diff --git a/STATUS.md b/STATUS.md new file mode 100644 index 0000000000000000000000000000000000000000..4efc74872b5e31ffc6c41b454001114d8b75ffe0 --- /dev/null +++ b/STATUS.md @@ -0,0 +1,7 @@ +# camara mirror status + +State: complete mirror + +- Original files: 760 +- Marked documents: 760 +- Missing marked documents: 0 diff --git a/manifest.jsonl b/manifest.jsonl new file mode 100644 index 0000000000000000000000000000000000000000..f0c6c0d7dea4b2176a235a2c948b01dc8d4b7de5 --- /dev/null +++ b/manifest.jsonl @@ -0,0 +1,760 @@ +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointDiscovery/README/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/README.md", "original_path": "ApplicationEndpointDiscovery/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4fdc26ffccb7cebd28ef5c9fab5b38e47e018aa2f67959f8267415a7faead853"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery.yaml", "original_path": "ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9667b1934c01d2f71a5dcf2ad2b809dfe6aac92366500669b84ad9c83035399a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist.md", "original_path": "ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b4b603b319100404d10072802a1394f7ff46c9a17902ccc5b906cf6f7b7fd184"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointDiscovery/documentation/API_documentation/README/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/documentation/API_documentation/README.MD", "original_path": "ApplicationEndpointDiscovery/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story.md", "original_path": "ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2ed6d553b52f6be2293aa724b6a513667fdb459a37ad88b5beaa3c5baaf747f4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README.MD", "original_path": "ApplicationEndpointDiscovery/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/README/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/README.md", "original_path": "ApplicationEndpointRegistration/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f418aacae313647a40171aba505a936783b13c67f1b4a5b415eefc3ece257e82"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/code/API_definitions/README/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/code/API_definitions/README.MD", "original_path": "ApplicationEndpointRegistration/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration.yaml", "original_path": "ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d4802a61f8a62640fde4aab48cb8249f653087ed1c569e8bf70859a07e141603"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist.md", "original_path": "ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d140ad2da18c0d50538050a0a4f36a6bcff87b310b31ccecb484bebe122ecd2d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/documentation/API_documentation/README/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/documentation/API_documentation/README.MD", "original_path": "ApplicationEndpointRegistration/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story.md", "original_path": "ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "17aa4d62dd26a52db47a79ea86e223d4aec0f0254c145370e372501f43be5d9a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationEndpointRegistration/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ApplicationEndpointRegistration/documentation/SupportingDocuments/README.MD", "original_path": "ApplicationEndpointRegistration/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/README/raw.md", "normalized_path": "original/ApplicationProfiles/README.md", "original_path": "ApplicationProfiles/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "faecf9128fa80ab8ef4bfce1237ea2cdfd08170e59a853e00eb9944d66d275cd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/code/API_definitions/README/raw.md", "normalized_path": "original/ApplicationProfiles/code/API_definitions/README.MD", "original_path": "ApplicationProfiles/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ApplicationProfiles/code/API_definitions/application-profiles/raw.md", "normalized_path": "original/ApplicationProfiles/code/API_definitions/application-profiles.yaml", "original_path": "ApplicationProfiles/code/API_definitions/application-profiles.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8baabff6555096cc8f4b8ca4dc6e243387d6ba0a04f9096558ec58876a864d26"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/documentation/API_documentation/README/raw.md", "normalized_path": "original/ApplicationProfiles/documentation/API_documentation/README.MD", "original_path": "ApplicationProfiles/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist/raw.md", "normalized_path": "original/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist.md", "original_path": "ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b5be874e9e1517cb34a1cc1787e4ad0f5758394243a2651b3826954aac89d84e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story/raw.md", "normalized_path": "original/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story.md", "original_path": "ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b1a7e9db5a6f59f819f9bef3ed7ee95b9aa32c3bbcedac4df5523f09dc88ba04"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ApplicationProfiles/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ApplicationProfiles/documentation/SupportingDocuments/README.MD", "original_path": "ApplicationProfiles/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/README/raw.md", "normalized_path": "original/BlockchainPublicAddress/README.md", "original_path": "BlockchainPublicAddress/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ad6d00d0bb06f6ee90e2b87ccae2dae906a2521312f16f706f621e0eb4f91f6f"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation/raw.md", "normalized_path": "original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation.yaml", "original_path": "BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55004ada12751dac56f3ce8f5636f4619f71b2be1e780166be278a81b412938a"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address/raw.md", "normalized_path": "original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address.yaml", "original_path": "BlockchainPublicAddress/code/API_definitions/blockchain-public-address.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2562042dfdfd160d3a81297484f6f5959a5775b21e7facacb0a31b740e30df4f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist.md", "original_path": "BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0cde29bf8e2b3a61ec748fdbceeb53eca6c01b3d2a462f93c8822d0221a98594"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story.md", "original_path": "BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a8ea15c6493c1224947657e4903e7a1ee9b51d3dbd78f80db80e33c802db4679"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist.md", "original_path": "BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "08eb8f13baf2310b2d98327a44765023e361f9b81f896ccce6c22a9edbb43c97"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story.md", "original_path": "BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "914353aad03b42577790028087675bd7e25c87d0e46bd8c3b5e98e1799c9f917"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d8173d0dd266c8968fb1faa94653066a13a12b72cccb8bba03e4f5eb638fb349"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1b73596046ac3a44e3e6c4a16e930272ed1a1b155a7e4faf69169b83764e8899"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "402cd621deaf27fc5425ff4cfb77be7fdb76338742ba80bdcb77dfa39838ccc7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ab3bc429bf830c50888ac2fd8f3bb7f56c87d1c3746f14ee5e5e3126112305ea"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c7d8d315eca2f1565c76bfbd63b2e1c165d06a7a4843957924f407b49d2bd516"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2094c9885594ff4ac7cccfc6c360362c3bb2f8597a5362c0ccdda0ffaf787df4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "52306d4b52354145cd6a5e753975d343db9c6d031a684a2925274bb57eb2ddfa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "52f5c187f90b8f92e297891006979ac12d87b7bb58b751225250c77f3d19fe94"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1be253774492dce60b7cc12e02a5fb406dfc3d909a251f66d683fbbcc750687f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1f94b477c169e159ca40173062dab7f096b9f618a870ea0860f694c864d9bdc1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "33f7489171b1458414aaceca66e6f28855758965dd53773558c45e7fb0dd0d89"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "52385860638fd186c48e18763db156977b2e6e644d407509c8b58b527256c3b5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "675954390e98bbeb9e1c9c832d8f7b97fa8f564c507e142cebe48e343a2a17b7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9d2bd6f51547611723d67c094cf7b1e30523bf5b263b715bdd37892abb16024a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07.md", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "588d8b6f0bd51007ac2958c966202d4d04359182eab2264f6bb0ea1ef48afaa9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/MeetingMinutes/README.MD", "original_path": "BlockchainPublicAddress/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ac7816d146a12e589fa94f5a33395f8804f40c142b85fa416d4a5f528d9a9260"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/BlockchainPublicAddress/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/BlockchainPublicAddress/documentation/SupportingDocuments/README.MD", "original_path": "BlockchainPublicAddress/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CallForwardingSignal/README/raw.md", "normalized_path": "original/CallForwardingSignal/README.md", "original_path": "CallForwardingSignal/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f81d93b2aaf1cd83d05ded95ad67cf55ac0f03cb3e38fd9ec647ba88c00bebe9"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CallForwardingSignal/code/API_definitions/call-forwarding-signal/raw.md", "normalized_path": "original/CallForwardingSignal/code/API_definitions/call-forwarding-signal.yaml", "original_path": "CallForwardingSignal/code/API_definitions/call-forwarding-signal.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5fde9b6bbae7a437adde6a3d18a6e418e66df8b352f9c880db711b89e72951d5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1/raw.md", "normalized_path": "original/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1.md", "original_path": "CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "892f69c4c5404e132be8a868ca8786fff5ee4c0888748137f66199dcfd91181c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist/raw.md", "normalized_path": "original/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist.md", "original_path": "CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d66d62027158efa199a40f20f8fc05bc4955b72c76ae4ef5fca8ca5e322c1aa0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CallForwardingSignal/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/CallForwardingSignal/documentation/MeetingMinutes/README.md", "original_path": "CallForwardingSignal/documentation/MeetingMinutes/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7b8aa3245381163574da606199b6d144559f03a978247fe96a220bf9033abf82"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CallForwardingSignal/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/CallForwardingSignal/documentation/SupportingDocuments/README.MD", "original_path": "CallForwardingSignal/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/README/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/README.md", "original_path": "CapabilitiesAndRuntimeRestrictions/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "60f57da5e42083bfcafdc9f332350dc6577948b4c466f31ebb70ebd21fda4c7c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README.MD", "original_path": "CapabilitiesAndRuntimeRestrictions/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi.yaml", "original_path": "CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b7cbe8793a5325a55fde8dda5e74a02ca6a3d7dc655dcfa12e51fe5bc06b66a4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README.MD", "original_path": "CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories.md", "original_path": "CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "578d60328f313118e2c0ab8b689fd1bdd85105d64df9a629ddcf03322925cda0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README.MD", "original_path": "CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/README/raw.md", "normalized_path": "original/CarrierBillingCheckOut/README.md", "original_path": "CarrierBillingCheckOut/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ad51c3830570c8b5595c8b310ddd94eb69e4dfff043d990a5e67e0eb28f88d22"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund/raw.md", "normalized_path": "original/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund.yaml", "original_path": "CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6bea03af974ac8f78984a407dbadd44a5a4fb015ebb8544ca3d433d997a75d2a"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing/raw.md", "normalized_path": "original/CarrierBillingCheckOut/code/API_definitions/carrier-billing.yaml", "original_path": "CarrierBillingCheckOut/code/API_definitions/carrier-billing.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9e51057fb3c0894d4590b8b2f47b2eddd457118f49646c6017a6ca96ade8d6b8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "783c1aafff4d2afd29309ba03f180059cf9b12c8cd6a60ec431b5c3153795a41"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a73241b8e27e29b203f0e57f1b736e96b7677d6d8177ca7740a9ab087273d8b1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f6993179f00588e48beb439650d4851dea202f462b4adf887dbcf4819e773683"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "847ed31da026ddece9639c381df51c9dfe6e8c80cfe0a151700c3fbb7164c798"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "099b6ffd4de2d0d172fa1e5abcbdbd8cb97e247149fbb751af678c9f188bbf6b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story.md", "original_path": "CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "29abe0a12ff2940461c9dbb16858992abfb18621ccc73c7dcb1b5f774793a59c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9a0b990539e68a0bd3c9f228ccc18a954c297896cf86761e70a99bcf1a9b3d72"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "057f1770060bc683d1d5b797c2b540c2f828075644522981e95ae543dd5297f3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "39f86cab4834b3b3ff7eb1e382eb4a36feaf965d633e273aa63169dcbc3578ee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9f4c99b7fc73172e2683e86b6934c6c15fda576b03a466dd668344e7247874fe"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1630817d8cbbc8f643ef3649800cbf3b74ab39777ed8e29f6467b15ed1b79a96"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c5016ce5ab1c6bd422f733ece53465393e79e9cc4c01f047f91b35f1ece1cb18"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9fc87c67f93fe824cc844262342b53ffd304ede43cd98c89b5d8c3bb20d8c4e2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7f0e870b05115b293ed7b786ad4366815a1fbe2c418f1d4d2b02ddd3cdd4d063"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "44d54c8f49a8686dd9fb4ff796027c11a1d16d7d6cc77da9ce7450d6406dd016"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8bdd3bb911ec83e8973319c61ccfc882036fe886a24e27d646afdf1d83794e4f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "49aedb55cffe045118fe9b41693095b419470f20b9f6a8a1915559323c12080e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6bd3cb0f780673accaeee5ad066049c8041d4e0a7653027ffac301c6af6b19c7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d6a97ad62ae0647fddac9e736c5f6a725fbb0467c0477c37fd98b8beaab8f81"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ccf26cfc95677265772eded63a38b3714a248b71f63bd28f3005aa2abd01a2f2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3112ef1909ace67618e199201b7bac058cf33a0bd71516f2cf22ce4568e2e17b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "32233366f35993bc8f3c4240c3ede14e75fde81088e707c0397cc175ca9ea9ef"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0fb05ad5fc5e3fd9e29c9a3b425150cb528453cea335cf1968d6a05d95bfd214"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "69139e8377bb7f7d95a3493f697d9a7ae367e80c52d055a9577b72a8e0246fcd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b37ba760d216e4f91da0a1266df58b0836c17b8e36d4fb01a18f8cb26207c932"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3583c50038a89a6c0d1c110ec8cbe8510842bbb141e4878eef9198f3482631df"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "dbef9bea46855c73248917072d76b38fb0238d04b008e3ad260a4055f6b215f9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5fba4fd589c1848bf6804d3320ee4a655ba619901257869aed9829a3422968a7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0e52160c0833e43e5ce3c10785a5117e41ce1abfcd7c28c1db9b23ce05e53897"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7422800cd9508a618567cd1468d07963c621ca1eef5c2ded98d626501fe2f9b5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "93d5a3fa80628e98d084e95466513b2207a697529bd5e5bc81d015f21464db2d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "af35cf3ca0199f4e62eb264cc74a4b8270a51ef49cafde74867a4caa9b3dcc0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "954a6b17d781ab491cbfd7424ad67fff9ce65be6c241edd25eaec645d4b66779"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ffe1c6f3a2c098b6ebeec290299866c12e85ee20d93f3670a646c58211c63bf1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "633aa7dd91f6fe0a21cbdb22c45286b083825f16a7f3c97ffa6be971ade5faee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "19cbaae425f72dfe549e48313911f278b708cdfdd06b86a31f82499d9e9c60f4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "149f22183027683f524e61434a428cfddab0cb294f3f0f3e52f5666f5585ee7a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0f3a5690dac54915bd71e83e0105cb546b9894091f68e401147c721eb91599a3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cdcdfc44f1b3a38d14d0648dfc4203a0083c0a8800d632f0a5f178f939d62880"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4e6a68ec2be30ff42afa93ea38bcd5449218922cf79613e53bb598cc78aca039"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20.md", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cf9980cfe1c8a46a9a2d99c3f5535277ecd1840b1532b0f6d721264cdda8af58"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/MeetingMinutes/README.MD", "original_path": "CarrierBillingCheckOut/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "959cab2c9c4dde0476337de531c94dc26469f90d096b1d3b94fc2672191ab165"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction.md", "original_path": "CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4a4effaa021aedb6bfffe273547da6edca316bfa92838293bcb7267e6e3295b6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CarrierBillingCheckOut/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/SupportingDocuments/README.MD", "original_path": "CarrierBillingCheckOut/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bc9eed7df13c8b7518889eea74a9ea7996fa409a6540f837f40338175f9f105a"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout.yaml", "original_path": "CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "92a92b6de5df8863220d889b41a2ebe6c795ac598b6e535316e0bfff094b0ab7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment/raw.md", "normalized_path": "original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment.yaml", "original_path": "CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "83f205bd2a850454c5ce6d3046d805dacc816c14c1b3ef59b2d8d412f3d946f8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/README/raw.md", "normalized_path": "original/ClickToDial/README.md", "original_path": "ClickToDial/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "501e78da11c598461b2674b4d89bf8110de0d7a9eb2a469d4bd63624f74ebbdc"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ClickToDial/code/API_definitions/click-to-dial/raw.md", "normalized_path": "original/ClickToDial/code/API_definitions/click-to-dial.yaml", "original_path": "ClickToDial/code/API_definitions/click-to-dial.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0e271484826a0bdc8fc82d08f438df8cf23297fb4fd2cd137ff5ac6278484c61"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/documentation/API_documentation/click-to-dial_API/raw.md", "normalized_path": "original/ClickToDial/documentation/API_documentation/click-to-dial_API.md", "original_path": "ClickToDial/documentation/API_documentation/click-to-dial_API.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a4180a07bc3f894b40b1b8d6e1ae53235c59e3fda9813fd00c1a8934c6ec2a02"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/documentation/API_documentation/click-to-dial_User_Story/raw.md", "normalized_path": "original/ClickToDial/documentation/API_documentation/click-to-dial_User_Story.md", "original_path": "ClickToDial/documentation/API_documentation/click-to-dial_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8dd6b7a4bba31537f9e8e359974a0262943b434fa8483bf5711837d86170e54e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10/raw.md", "normalized_path": "original/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10.md", "original_path": "ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7f71e519a24f2626ab43c59694998729eba59418422abcb5da4c259911d9c092"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/ClickToDial/documentation/MeetingMinutes/README.MD", "original_path": "ClickToDial/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ClickToDial/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ClickToDial/documentation/SupportingDocuments/README.MD", "original_path": "ClickToDial/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectedNetworkType/README/raw.md", "normalized_path": "original/ConnectedNetworkType/README.md", "original_path": "ConnectedNetworkType/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ff263d5378dbd39d074c91335ef637c8ac0069cf4c1bf493636a887a26cea711"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions/raw.md", "normalized_path": "original/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions.yaml", "original_path": "ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0dee4eb058b8672f38b9d33d73330205d5845f5411aefc40b9a6306df0a410ff"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConnectedNetworkType/code/API_definitions/connected-network-type/raw.md", "normalized_path": "original/ConnectedNetworkType/code/API_definitions/connected-network-type.yaml", "original_path": "ConnectedNetworkType/code/API_definitions/connected-network-type.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "65b5db98c31abfcd54bef30c86736fd02919b240518aa7f5bc05d9e2691a7d6a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md", "normalized_path": "original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md", "original_path": "ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "587c42456b9dd92b0693ea786940501bf6141bb29040b17dcd243a2494bd15a3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md", "original_path": "ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "012fa833c313395194719408b31c28c9a7fd20a9d7bcf1f0328a27fe4604922c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectedNetworkType/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ConnectedNetworkType/documentation/SupportingDocuments/README.MD", "original_path": "ConnectedNetworkType/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/README/raw.md", "normalized_path": "original/ConnectivityInsights/README.md", "original_path": "ConnectivityInsights/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "21b07beaa584d9dca98860431e955d888e5710ce1ace989cde69ea0ca76c13ea"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions/raw.md", "normalized_path": "original/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions.yaml", "original_path": "ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c6b1a46dcc61a2cae6a4771666c0f3ae953e237cdda6a4d83389a0b0a1a6330e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConnectivityInsights/code/API_definitions/connectivity-insights/raw.md", "normalized_path": "original/ConnectivityInsights/code/API_definitions/connectivity-insights.yaml", "original_path": "ConnectivityInsights/code/API_definitions/connectivity-insights.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4f2c4bb89888dd63f3a1f2d35e9db1773d9a994f183624c8294aad33b2f43862"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist.md", "original_path": "ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c43246a979eb822775a86a10635c1baf88c1467f457ec77e63358caa4b908dfb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story.md", "original_path": "ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "af04f11386fb5b4b0e0c785788e0166d6395498bae71dcc837a53decf1483bd6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist.md", "original_path": "ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e36d6255e50598237dc6802f3bdb6c7429912b36dba8e765925af6c84389c6e9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06.md", "original_path": "ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cacdb3c147bedf6d5397a76bdeb6082e40b3b3fecfd3265533d31008b67b1eef"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13.md", "original_path": "ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d2a859036ff2c39c95598035ef3abcc8eb8d3f9c78bda3e68dbef5cf432de802"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20.md", "original_path": "ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "549d3984a40294af71bb5ae73a6608ac42d46b8d3393185192a867e1af50c22f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19.md", "original_path": "ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5ee51e2172f5661a12cd633d9d58fc8625e9195ec842fa4396b39ce3c1532316"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/MeetingMinutes/README.MD", "original_path": "ConnectivityInsights/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConnectivityInsights/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ConnectivityInsights/documentation/SupportingDocuments/README.MD", "original_path": "ConnectivityInsights/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConsentInfo/README/raw.md", "normalized_path": "original/ConsentInfo/README.md", "original_path": "ConsentInfo/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bbcc81d608b9dd87a864ae96c36fe072e823a7a5f86f4631b4d0e6b921b1a77c"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConsentInfo/code/API_definitions/consent-info/raw.md", "normalized_path": "original/ConsentInfo/code/API_definitions/consent-info.yaml", "original_path": "ConsentInfo/code/API_definitions/consent-info.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "61a043e7142221b8a03cec52f35430712432d02d489c7b8e74e1dfdcfed892df"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConsentInfo/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ConsentInfo/documentation/SupportingDocuments/README.MD", "original_path": "ConsentInfo/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConsentManagement/README/raw.md", "normalized_path": "original/ConsentManagement/README.md", "original_path": "ConsentManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e9b09dbe642960120106be2a9eb8d5a76ae9224408e1a2b21e4070849225fc57"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ConsentManagement/code/API_definitions/consent-management/raw.md", "normalized_path": "original/ConsentManagement/code/API_definitions/consent-management.yaml", "original_path": "ConsentManagement/code/API_definitions/consent-management.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bb723265f4ffef7b814edbb0e2249bdc41bdae3cb6a8c84fb11914bb30bd970f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConsentManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/ConsentManagement/documentation/API_documentation/README.MD", "original_path": "ConsentManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ConsentManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ConsentManagement/documentation/SupportingDocuments/README.MD", "original_path": "ConsentManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CustomerInsights/README/raw.md", "normalized_path": "original/CustomerInsights/README.md", "original_path": "CustomerInsights/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "02ae84ec8bebd29ac3f22a7d752e06919f3a267f77412be84d18b231c82f2401"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/CustomerInsights/code/API_definitions/customer-insights/raw.md", "normalized_path": "original/CustomerInsights/code/API_definitions/customer-insights.yaml", "original_path": "CustomerInsights/code/API_definitions/customer-insights.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "809895b031565533ec165d6cb8fa2caa21ec40932ef708f10cd633fb24356096"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist/raw.md", "normalized_path": "original/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist.md", "original_path": "CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e49752fca8ce8e92ce01911fb8564a7481f605fcae5d157d9af8e64955808d18"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CustomerInsights/documentation/API_documentation/customer-insights-User-Story/raw.md", "normalized_path": "original/CustomerInsights/documentation/API_documentation/customer-insights-User-Story.md", "original_path": "CustomerInsights/documentation/API_documentation/customer-insights-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "86e569baa7c7542f20fe3b5e262d650246f453802ae3d2c83878144c8807f348"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition/raw.md", "normalized_path": "original/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition.md", "original_path": "CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "23dd815e1565fa11e07b4aeac10f2bb0c0099dd6a751b633cf61d7b6c8e24e9b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/CustomerInsights/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/CustomerInsights/documentation/SupportingDocuments/README.MD", "original_path": "CustomerInsights/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/README/raw.md", "normalized_path": "original/DedicatedNetworks/README.md", "original_path": "DedicatedNetworks/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c709909ef8075bf195316156286a30d9fb1dd4dae6976e3bfdb5ee5f4e75e14e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DedicatedNetworks/code/API_definitions/dedicated-network-accesses/raw.md", "normalized_path": "original/DedicatedNetworks/code/API_definitions/dedicated-network-accesses.yaml", "original_path": "DedicatedNetworks/code/API_definitions/dedicated-network-accesses.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "787acbe3fa5ef1b5c23f2feb231bff54da4354be734ed1687faf0f70de7009b4"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DedicatedNetworks/code/API_definitions/dedicated-network-areas/raw.md", "normalized_path": "original/DedicatedNetworks/code/API_definitions/dedicated-network-areas.yaml", "original_path": "DedicatedNetworks/code/API_definitions/dedicated-network-areas.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b24582d9bada9710043dc026c7503803bf553e3659970c6d62fe4da24808e820"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DedicatedNetworks/code/API_definitions/dedicated-network-profiles/raw.md", "normalized_path": "original/DedicatedNetworks/code/API_definitions/dedicated-network-profiles.yaml", "original_path": "DedicatedNetworks/code/API_definitions/dedicated-network-profiles.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b0e374e13d0dde3451d37e105e2a9a36d7fe56477784c1ac2c9bd12c8fe12cc1"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DedicatedNetworks/code/API_definitions/dedicated-network/raw.md", "normalized_path": "original/DedicatedNetworks/code/API_definitions/dedicated-network.yaml", "original_path": "DedicatedNetworks/code/API_definitions/dedicated-network.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "915f1a276a385254423d0e85ab9c3a657860cad9eebff108208e3c89c10276fb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md", "original_path": "DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2c053b557a9cc2904c67f50b2703257c59c3fce62283a8bc3eea73010e09bb6d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist.md", "original_path": "DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b95c5a20ce9cf0d4ac8d766e8773fb988b155a3fd64e5af68625ee6204a33098"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist.md", "original_path": "DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "05dd36ef3349924decf353d11d80649f4b65d47c6be9f44389ea31ab49455ae7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist.md", "original_path": "DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "65425ea7142379716d5cc9b38719c24393a1efaae150718caa804542eb347725"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/SupportingDocuments/README.MD", "original_path": "DedicatedNetworks/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios/raw.md", "normalized_path": "original/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios.md", "original_path": "DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d4197d7cc12e34583fc2950688b752c982cd87eb1425eaa6a165427c2dcdd00e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceAuthenticity/README/raw.md", "normalized_path": "original/DeviceAuthenticity/README.md", "original_path": "DeviceAuthenticity/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c3c147d7e493c652a0a48c5a626ee5e96a1fc9731b22439499e26e65321b2a42"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS/raw.md", "normalized_path": "original/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS.yaml", "original_path": "DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d95546377fa52f760b7705d5e23577d561abea084d24152a7db9f4ecc9ed814e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceAuthenticity/code/API_definitions/README/raw.md", "normalized_path": "original/DeviceAuthenticity/code/API_definitions/README.MD", "original_path": "DeviceAuthenticity/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceAuthenticity/documentation/API_documentation/README/raw.md", "normalized_path": "original/DeviceAuthenticity/documentation/API_documentation/README.MD", "original_path": "DeviceAuthenticity/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceAuthenticity/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceAuthenticity/documentation/SupportingDocuments/README.MD", "original_path": "DeviceAuthenticity/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceDataVolume/README/raw.md", "normalized_path": "original/DeviceDataVolume/README.md", "original_path": "DeviceDataVolume/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c87b30b551afabcae7ac850d6afe918029f77506e78853ce688da4d39715679d"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions/raw.md", "normalized_path": "original/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions.yaml", "original_path": "DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c657f27d329bbda59d57d77613e203d31d336c352965e53557d820b4ce37a199"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceDataVolume/code/API_definitions/device-data-volume/raw.md", "normalized_path": "original/DeviceDataVolume/code/API_definitions/device-data-volume.yaml", "original_path": "DeviceDataVolume/code/API_definitions/device-data-volume.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1b1aad4b8adec429432c38083e149c4e75ca3d020566dfcdac992933dca00220"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist.md", "original_path": "DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6a15643c3f416a39ea15a933d5f91d0ea6ae172c818495b97d2b59062ddf5fbd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a64bb99f29502d0191e5bf8c822cc59e7ca35b632e72482e131d95ffc2e930cc"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceDataVolume/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceDataVolume/documentation/SupportingDocuments/README.MD", "original_path": "DeviceDataVolume/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/README/raw.md", "normalized_path": "original/DeviceIdentifier/README.md", "original_path": "DeviceIdentifier/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9367fadcdd9ff7a802636d39aa9411ea84659bc060dd9edef9af297a5a6c0b7b"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceIdentifier/code/API_definitions/device-identifier/raw.md", "normalized_path": "original/DeviceIdentifier/code/API_definitions/device-identifier.yaml", "original_path": "DeviceIdentifier/code/API_definitions/device-identifier.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "63a29be7875e7f059b743ce8bda273badc3b2a69da066a65853c1092ba7b1daa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story.md", "original_path": "DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8657a18a89502f0e9f3bcab41bf42894e7edb9b2035eb6a5817b9fbbaf4ed048"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist.md", "original_path": "DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "65b1d7a18aa33f4742576a1bf4a74db2a6e9cf2a7cc9537fb02d0124cbd49a61"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "96ae15e17bf8f7fa665cb61fbbda2464649c2fbd018a4a6dd00889565e1a5362"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "01748f8cbe12907ace37de8f277755b6880384db789d2e3fddd4701ac060fcd8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ad30db72f3dd247ee9dc3d5072540aa6aa879a6615ea77dd283ab7558807c79"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "20b4b52dc1049400d224876d0bf05bd5f88eee225ae2b6225b7cf1355d048b9c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c3c18109b8181a54796018483712bc2c8acf044f64f15e443ce57689737570d5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b054f2d0505819e0b0c2d8360fc37ed13439df0c1e1304aa753903623359458d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7cabb4cad3791846b19da768130f682512cd17e1a81ff7d0bde77948d0da1c23"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5bb562093be5245558d54673a6d59bc548ab2bbf0057479c4f72ebe9c61f37b9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b53260c648429c4238b40edd4f3e181a6b1adfe631cba04cf14791ca0f08cd21"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "79a17e9693c5aa19e0c7f14e5a4c46753dbaf9c4a396b8f5de660508ff2a506f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4f01f47de67db96112712f978c64afe96a0282dc51e3e28c661c102ee6d7c148"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "746cda57d2c5f954f9b6dfc65e2a55281eb101b03f18ef3897f48049ec22e126"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/MeetingMinutes/README.md", "original_path": "DeviceIdentifier/documentation/MeetingMinutes/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "84e9d8dce4fc0c089abe89fc6823107ebb1205d269498f8104d93c151162fbf4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceIdentifier/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceIdentifier/documentation/SupportingDocuments/README.MD", "original_path": "DeviceIdentifier/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bc9eed7df13c8b7518889eea74a9ea7996fa409a6540f837f40338175f9f105a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/README/raw.md", "normalized_path": "original/DeviceLocation/README.md", "original_path": "DeviceLocation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "eb5c1bb4c7a35e8bf480aecd04ae4fd029a1877d9d7c7cb7413ae1139344e612"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceLocation/code/API_definitions/geofencing-subscriptions/raw.md", "normalized_path": "original/DeviceLocation/code/API_definitions/geofencing-subscriptions.yaml", "original_path": "DeviceLocation/code/API_definitions/geofencing-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0f7c79fa553477228762fc19349153a0e51f048570feb8a87491d9f30e693a59"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceLocation/code/API_definitions/location-retrieval/raw.md", "normalized_path": "original/DeviceLocation/code/API_definitions/location-retrieval.yaml", "original_path": "DeviceLocation/code/API_definitions/location-retrieval.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "224db0cd161e105e2c074b445caeaa4f6f811273c6e42b9b4714fc6a98589ab0"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceLocation/code/API_definitions/location-verification/raw.md", "normalized_path": "original/DeviceLocation/code/API_definitions/location-verification.yaml", "original_path": "DeviceLocation/code/API_definitions/location-verification.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7fe45ccb77420ffe728c835143af369ad794076589066a3abdb764840c23f70e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1b556b4314d36cadb9b3afad54ce4fc2bc31d2b2f9d5274a4e9ae1a99ffd29ce"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist.md", "original_path": "DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "83c09e630dfd48c1f5f540ecc6e9ba71a91dfb2dbb076927f24cb81f586d2cf2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist.md", "original_path": "DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2ab09d70fa7f4f301aa32603b9a489827a98b8279d0278015a84ee35ce600817"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/API_documentation/location-verification-User-Story/raw.md", "normalized_path": "original/DeviceLocation/documentation/API_documentation/location-verification-User-Story.md", "original_path": "DeviceLocation/documentation/API_documentation/location-verification-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8b602f63766716928ed20e46ed58696198c833627b58450f4f6bd86de2c8e847"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "06e021c86627087213566da856d553ca2973f88a0f2ecae7fcc4b041adf40893"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "732855058812a40711e437c98150c7f26316d59ba0b263a6c24c7aa1184edc38"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b17d90e3bbe243d69f9fd9bed0ea833345e48a4712ac11ccbdcd41742389199f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4c5744d353831b530885904d8e7e7da3bcb0944d0e6e059fc64a702dc321f16b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "adb6aa0da88526f668034280ac63a07f60138ec8db8e11ebea332937a9e21833"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9a24a7433b176e213ed19fb40da942091ceedb70caa1a4ea0e585c91be097565"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0c024a02abba031dc215ae34a23fdddf32214e7b78974ed22faa2dbe4e88115e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c0d17e3603f42afb54487cd9d874ffefe7b4ee3ba972c48f3c5a3819b0893d12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a403604d471d7b7011272cf4265fbc20ced4c1b2bf41223c641963d628dfce71"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9e67db9e333d79f4c37ec6429a391ad2f5e2bb62a7732c576d9e1ad4dc180f98"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "37f65e0cddf2b915a2ae1bfa8fa590e550957a4740dff3e79e2a727161a5ad00"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fa444f2bdd5d770af92178a48e5dc683064eeace15e5290d49d556165688ffa7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e58d8bdea5177fff2227d384d9ad81236d800d9c545008b631419fd391e83648"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "589dd6a8d557761a7ce0bc9d7251cb716029a793f105c33507f3d31f429429e4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e3b53b3405e69d8b5b65d4cfe2754ceb90a2632f6f52dff24f66aef56554fcab"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "766e91694d8aeabd060370ea62e56f897c61cf2604a34618d89ffa27a43c60bd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "615d34bbd3e06b975433cd445618b799cb492e21b749ee0b91980f267659177c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5a8a63dc4562f8cc8b336ac188166cd2158232b7d7d42e7d5fde64316b86dc5d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b841b523e40834cd0fd1cbf5c353c460ee2e0d71458c199b8d89439cb02488ba"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d61a7598795868cc958dba005d81f326ceb5dc11f94b1f3755f913923ee53229"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "67c5dcdb58ee2365dd701686cfb4ed3b0134334e78fa1e06579791db4336ab76"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9fc4d2790bae6b2f677288593ef98a5bb4f93e967403baec2c6aff9225215b55"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "df14afa79312a0d0f5b5bb737f0230a5d40cf1e6bda16539ea27c6aaeb34b9ba"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fa10a1c3870d6ffcd0f4d9d59c9934c84ccf9cb75a01a77472e4187c25297a16"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1302238bb4ba426e288d5cc5ad97d1ae935e5bf4b22f8624fe97bcc4fd09a91e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "03e136fb1c5050f126eb76a3ded9f4fef6234981be04118ad069270049eaf651"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12/raw.md", "normalized_path": "original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12.md", "original_path": "DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fdece868b2a351c440b5afe9d7bdf3992725069a9a21a69c3d3d7565d793c172"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceLocation/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceLocation/documentation/SupportingDocuments/README.MD", "original_path": "DeviceLocation/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceMediaStreamingRate/README/raw.md", "normalized_path": "original/DeviceMediaStreamingRate/README.md", "original_path": "DeviceMediaStreamingRate/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c4ed96ab57d46e67289a2c730831006e17cc3520c319cf3ed95cc23c5d1ebf81"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceMediaStreamingRate/code/API_definitions/README/raw.md", "normalized_path": "original/DeviceMediaStreamingRate/code/API_definitions/README.MD", "original_path": "DeviceMediaStreamingRate/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate/raw.md", "normalized_path": "original/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate.yaml", "original_path": "DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2e0f54672556863c6c8c22081c83408052df5b59bafa682c4f9e6de6d31da53a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceMediaStreamingRate/documentation/API_documentation/README/raw.md", "normalized_path": "original/DeviceMediaStreamingRate/documentation/API_documentation/README.MD", "original_path": "DeviceMediaStreamingRate/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceMediaStreamingRate/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceMediaStreamingRate/documentation/SupportingDocuments/README.MD", "original_path": "DeviceMediaStreamingRate/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceReachabilityStatus/README/raw.md", "normalized_path": "original/DeviceReachabilityStatus/README.md", "original_path": "DeviceReachabilityStatus/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4347544d3a585f63ccb5c2432f6a2781448deae1b8bce2eedb87814366f010df"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md", "normalized_path": "original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions.yaml", "original_path": "DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c3353764d6c930dba74d81e88a2e206cb520ea3281b15ba803b074ec7a8a46a2"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status/raw.md", "normalized_path": "original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status.yaml", "original_path": "DeviceReachabilityStatus/code/API_definitions/device-reachability-status.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "56d59e9057bb62fbbbf2b1269eb1c1cba3d8f9ee49cc89c22b2bb7542ee1cb46"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md", "original_path": "DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d478263c7485695d15a04efa05f32daf9dc01b4b3e454d71b3f986b54a0ed2d6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md", "normalized_path": "original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story.md", "original_path": "DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2aa41540445c00895a833ffac55608d1cbe5eeed503ec77239e7e4aedca23153"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f75d934d804ec3c105020b5bf4c0275d8e5cf0609faed668dd3e72bdcac0c197"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceReachabilityStatus/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceReachabilityStatus/documentation/SupportingDocuments/README.MD", "original_path": "DeviceReachabilityStatus/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceRoamingStatus/README/raw.md", "normalized_path": "original/DeviceRoamingStatus/README.md", "original_path": "DeviceRoamingStatus/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7c69fde49bb1a581399b47e4a2eae33436d50a7ac4ddcb5eddb3e798b081dd8c"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md", "normalized_path": "original/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions.yaml", "original_path": "DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "28796c7aac15904b73de0480b879901e20f73ecad205c5e9a8bff50b25cb93b8"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status/raw.md", "normalized_path": "original/DeviceRoamingStatus/code/API_definitions/device-roaming-status.yaml", "original_path": "DeviceRoamingStatus/code/API_definitions/device-roaming-status.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fbc2036435f76c9e569d84657ae93d6fb6d91e98ffb3c1bbb135796e99e2820c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md", "original_path": "DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d9a3901165cc9ebc880ad5935e1da36ac277251bb1c83d0d85c40c651a1b8626"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md", "normalized_path": "original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story.md", "original_path": "DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "005a72193540a4839e2fd7d0aa3b06b3c371a5374e746ba91a0357b3b4a96fb5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b7ab5118ac7b3f66ef50e69dcb067158a3292327b12f7637e3064050062c6a31"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceRoamingStatus/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceRoamingStatus/documentation/SupportingDocuments/README.MD", "original_path": "DeviceRoamingStatus/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/README/raw.md", "normalized_path": "original/DeviceStatus/README.md", "original_path": "DeviceStatus/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a7551f776199f364212869fe18047562e508f9783336b6ee7188448fa82aaac9"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/connected-network-type-subscriptions/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/connected-network-type-subscriptions.yaml", "original_path": "DeviceStatus/code/API_definitions/connected-network-type-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ae7af726ff71f6b11f2f3a9aca0b58ed373076180e402dcb22dd5c2ffb1bfb55"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/connected-network-type/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/connected-network-type.yaml", "original_path": "DeviceStatus/code/API_definitions/connected-network-type.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "843f0afc941b5c8febe19f8b79a9bce9d24c989f0d9717a15935ee9e8794441e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions.yaml", "original_path": "DeviceStatus/code/API_definitions/device-reachability-status-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2a72f21ddd311de4dc39cc9fb05c7e6ede4d4166548aba0cb7ef7e012c239117"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/device-reachability-status/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/device-reachability-status.yaml", "original_path": "DeviceStatus/code/API_definitions/device-reachability-status.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1e2d02aca243b8630af2131033603ae956ce0ede09b8bc58fefaa3c9ebcbffb9"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions.yaml", "original_path": "DeviceStatus/code/API_definitions/device-roaming-status-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a8a3d46b2fb35746c9a363855fafaf3569ae5fdfe2a5744957da959e6c324136"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceStatus/code/API_definitions/device-roaming-status/raw.md", "normalized_path": "original/DeviceStatus/code/API_definitions/device-roaming-status.yaml", "original_path": "DeviceStatus/code/API_definitions/device-roaming-status.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "24b039952b70d629fd1246fc7005e858a40e794f86228a3f74ca38964756edc4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5c22b73cf34c11e4bc2969ff1efc0a33a8f76e750b8b5bc3221ee2c7ec8de35e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "67d0331e7da90773aee3728faf41b9495cd915f05c3e2fa9044719fbd46aabd6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0a2fdd4191f6b6636daf4006355385ddf3a7c974f82f674b2d4035f13c8fa99b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story.md", "original_path": "DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2aa41540445c00895a833ffac55608d1cbe5eeed503ec77239e7e4aedca23153"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ccf61721060a1338e4c769ad2ff957618ff8cd1f10f4e014ae8c6abeb937e4f8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2eec466d04cf3f32d4a68498f976f9aab44d4281234204668f988b74ddd3e901"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story.md", "original_path": "DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "005a72193540a4839e2fd7d0aa3b06b3c371a5374e746ba91a0357b3b4a96fb5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md", "original_path": "DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "95e997196ab776c7f3981ee562281694a7ead026cea6cad59e8593524ab76603"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/API_documentation/resources/README/raw.md", "normalized_path": "original/DeviceStatus/documentation/API_documentation/resources/README.MD", "original_path": "DeviceStatus/documentation/API_documentation/resources/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c8d8d800f094a097d197c98739b692474b9a2d87df9682eac04a705550ee6d2b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6e1e87b9947507a28fc3a923d535f5bc1078056f33aecd3b227064e4cad7a172"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f23cc6a21f2754a347e8eb8edd462cc9c5d7b1092a9e606d21459f11aaf6604b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6cc36f3a2917f7c4bf7c2e46908851b2d250e42e0a1c64c3cd874e576d20a631"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8c3b96401c4e8a932e91e971255bd5abbf3f3fc2399f4627baa147ecbb887209"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "35b4b5979ef12f6e15ee5c7bedf4729b83f3893136503609b4bc7463ff851d71"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5eef463b1ca6e86e9a17f67c0c36d614d7d0daeed22e9d947ba61db970cbcbf3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b2b918ecf69120d58faadea68da9a43947944c6e6f101954f43df9a3540c90ce"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2953469b83556c3cf5f96d6e942ee55dc41136147bfcf57db395387d718b53fb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f9d780462ab8942a16c5e9fef800237ea3e57c989a3fb62e4794007c0dd6793c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ca943a51a1b33f1d984e75147c0262908183f1e853c42f0882fb4aa8e9757ad3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5846129b41f2c215564ffe2436d61deceee6048926c3a03e515bfab0a4b736fb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f59018c14053e29fde49c863453681d991612c6dfd9726822f525dd157e9f6ac"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b55c053969a8171ec01460ab6d4c965db641c8d5a517a6a4058161711a5947d2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3243f38f7ef2329006875149dee16fe056d02f3cda7b00f0e92b9d48ecae0f23"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d87ab595fcc391d69bd474357df71bc46dd880d5b4b1f02da6a114840b8763bd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bb8b2da580354eff4858f3c76e97d257cb42c7148c1cb8b98ba148ee445fb0ac"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12.md", "original_path": "DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2742f0182700577ceabb65ef1c5a7c9bb07c0a91a1edc2184a97bfc5528e3cb5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/DeviceStatus/documentation/MeetingMinutes/README.MD", "original_path": "DeviceStatus/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceStatus/documentation/SupportingDocuments/README.MD", "original_path": "DeviceStatus/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone/raw.md", "normalized_path": "original/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone.md", "original_path": "DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e885a5b84605b12e91d8ff9139807d6308ed5caff5b3932d71d4d2af3e262de3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis/raw.md", "normalized_path": "original/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis.md", "original_path": "DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9706b8defeb55abc774fbf4f70fb64f194aa740e69c2f09e3d67c61afe7168a8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/README/raw.md", "normalized_path": "original/DeviceSwap/README.md", "original_path": "DeviceSwap/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d52e19b7883ec0ae3e2b8d491cfa1240e2f1587f7daae0ce3022aef9c781e319"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceSwap/code/API_definitions/device-swap/raw.md", "normalized_path": "original/DeviceSwap/code/API_definitions/device-swap.yaml", "original_path": "DeviceSwap/code/API_definitions/device-swap.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9dde9e41e2427243289d135dc55a25f04e00c40d2c4a5abf1a39dd4bd404877e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist/raw.md", "normalized_path": "original/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist.md", "original_path": "DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "882656ead3c46e981335fff267a4e47ee4c496d9ee708cc09c6103f11c48e59a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story/raw.md", "normalized_path": "original/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story.md", "original_path": "DeviceSwap/documentation/API_documentation/device-swap_check_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "64fbc662f39c815c70e9dab372af6a837118e366e795ec917875833a9355d5e0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story/raw.md", "normalized_path": "original/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story.md", "original_path": "DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cb2e9168b4fe18d9f1038607a27c6ce578e8f44fd9fea9f20d004b5b32aadef5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/DeviceSwap/documentation/MeetingMinutes/README.MD", "original_path": "DeviceSwap/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceSwap/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceSwap/documentation/SupportingDocuments/README.MD", "original_path": "DeviceSwap/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceVisitLocation/README/raw.md", "normalized_path": "original/DeviceVisitLocation/README.md", "original_path": "DeviceVisitLocation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ffe9b22db4ecf714439f5f3623bbd67e1e6f3313f0d6fd86532e49cad291efac"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/DeviceVisitLocation/code/API_definitions/device-visit-location/raw.md", "normalized_path": "original/DeviceVisitLocation/code/API_definitions/device-visit-location.yaml", "original_path": "DeviceVisitLocation/code/API_definitions/device-visit-location.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cfaedeed64427d987874e0cf326783ba342224a83a201c6bd482aa35b33cd2bd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceVisitLocation/documentation/API_documentation/README/raw.md", "normalized_path": "original/DeviceVisitLocation/documentation/API_documentation/README.MD", "original_path": "DeviceVisitLocation/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/DeviceVisitLocation/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/DeviceVisitLocation/documentation/SupportingDocuments/README.MD", "original_path": "DeviceVisitLocation/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeApplicationManagement/README/raw.md", "normalized_path": "original/EdgeApplicationManagement/README.md", "original_path": "EdgeApplicationManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8b5de438cc895678153d8ee3c214cd1ba03bd79637baa5f96633dab190f5e024"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeApplicationManagement/code/API_definitions/README/raw.md", "normalized_path": "original/EdgeApplicationManagement/code/API_definitions/README.MD", "original_path": "EdgeApplicationManagement/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeApplicationManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/EdgeApplicationManagement/documentation/API_documentation/README.MD", "original_path": "EdgeApplicationManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeApplicationManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/EdgeApplicationManagement/documentation/SupportingDocuments/README.MD", "original_path": "EdgeApplicationManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/README/raw.md", "normalized_path": "original/EdgeCloud/README.md", "original_path": "EdgeCloud/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9ee7db61766ec5de6f12aebb7b822090ae644175b432ffd46be3f0572ffea9f4"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/EdgeCloud/code/API_definitions/edge-application-management/raw.md", "normalized_path": "original/EdgeCloud/code/API_definitions/edge-application-management.yaml", "original_path": "EdgeCloud/code/API_definitions/edge-application-management.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "846eb55aa4dd47e9a354afd6ad359f93970a950d68f18196e56f3601938f264d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/API_documentation/README/raw.md", "normalized_path": "original/EdgeCloud/documentation/API_documentation/README.md", "original_path": "EdgeCloud/documentation/API_documentation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55c6ad07e2b314cdabdccb190ea63f60aebf8648b04902611ad642e5c68121ad"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story/raw.md", "normalized_path": "original/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story.md", "original_path": "EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d052e6a4f9c31ede448f02ad564dbd682491c6d6d54bac9ad951a1273e3a4905"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1d5cdb9927375f9d6d4a3b6e580aec69d3511ddf56fa944de9c2355ffea1e646"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2bf165d96d460369178a04a35f056d5ed75cc4ee2e3b4f201fc2844ce01f7ebc"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5e2d08c976cf4e2b8b7ba90854e93c11fa1fd7abbc804189fc930ebfc38efd73"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b039aa1a11e691e523231a942e05888adca18baa7a61fe85d87dc5ff3680c700"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e7d4a6f0003cc26aa91e8417948fbcf4c3b40c789c51fcf280586aff3972d170"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023.md", "original_path": "EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9828fb3c3ddd0a419e0f803e5a143f8b2b589c4387186b643400d8cf178bf597"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/EdgeCloud/documentation/MeetingMinutes/README.MD", "original_path": "EdgeCloud/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5f470fb700f2b4173d26c783c056bf98de5c6b1e417c2e2cfe6f54b700770fc2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README/raw.md", "normalized_path": "original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README.md", "original_path": "EdgeCloud/documentation/SupportingDocuments/API_Documentation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b1860b0a5b0a4cd7932d5bfb26bbc2c583c4358d5409044fb73a88febba60326"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story/raw.md", "normalized_path": "original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story.md", "original_path": "EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5399f7520881cdb92f464199ccfbab7a7e1d58edaf138738817cc02b24c24513"} +{"body": "camara", "file_type": ".json", "marked_path": "marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta/raw.md", "normalized_path": "original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta.json", "original_path": "EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta.json", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "506a214eed4e2194ba80eb8b1e6e8d60f74ec4ac9754d595779d5faad333e788"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation/raw.md", "normalized_path": "original/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation.md", "original_path": "EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e402dfbe635b171ecef84eb3d8f57d872b38a82cfeef10674c8780b4f115c3dd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EdgeCloud/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/EdgeCloud/documentation/SupportingDocuments/README.MD", "original_path": "EdgeCloud/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/README/raw.md", "normalized_path": "original/EnergyFootprintNotification/README.md", "original_path": "EnergyFootprintNotification/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "81d64598a0b656efc3e33cbbaf49e16b6c389b7e887a000dad898f932f1bb38f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/code/API_definitions/README/raw.md", "normalized_path": "original/EnergyFootprintNotification/code/API_definitions/README.MD", "original_path": "EnergyFootprintNotification/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification/raw.md", "normalized_path": "original/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification.yaml", "original_path": "EnergyFootprintNotification/code/API_definitions/energy-footprint-notification.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "01ef2e05f6b72c541ba5062ba1486277d2e51f308d2aeb07aacbc1291d1cb112"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1/raw.md", "normalized_path": "original/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1.md", "original_path": "EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "31f13323071e91a1ea10a559fabef02aa6263938071a60b4d82152425417735c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/documentation/API_documentation/README/raw.md", "normalized_path": "original/EnergyFootprintNotification/documentation/API_documentation/README.MD", "original_path": "EnergyFootprintNotification/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist/raw.md", "normalized_path": "original/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist.md", "original_path": "EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6a8a2d42bf7d58667bee70e9d1a13ab4b00b586136ea1b172b5db650c1b3a211"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/EnergyFootprintNotification/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/EnergyFootprintNotification/documentation/SupportingDocuments/README.MD", "original_path": "EnergyFootprintNotification/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HighThroughputElasticNetworks/README/raw.md", "normalized_path": "original/HighThroughputElasticNetworks/README.md", "original_path": "HighThroughputElasticNetworks/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0f517915bad164d795e139c7d6c731cfeeac10b0779cde39116fbf36f60e22d8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HighThroughputElasticNetworks/code/API_definitions/README/raw.md", "normalized_path": "original/HighThroughputElasticNetworks/code/API_definitions/README.MD", "original_path": "HighThroughputElasticNetworks/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HighThroughputElasticNetworks/documentation/API_documentation/README/raw.md", "normalized_path": "original/HighThroughputElasticNetworks/documentation/API_documentation/README.MD", "original_path": "HighThroughputElasticNetworks/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HighThroughputElasticNetworks/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/HighThroughputElasticNetworks/documentation/SupportingDocuments/README.MD", "original_path": "HighThroughputElasticNetworks/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/README/raw.md", "normalized_path": "original/HomeDevicesQoD/README.md", "original_path": "HomeDevicesQoD/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "23f9e5a0f12ce2820d850523249bebae2bf8286d21b840348f70ae061e8ac57b"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/HomeDevicesQoD/code/API_definitions/home-devices-qod/raw.md", "normalized_path": "original/HomeDevicesQoD/code/API_definitions/home-devices-qod.yaml", "original_path": "HomeDevicesQoD/code/API_definitions/home-devices-qod.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e62186f6abc2b82590782897c4b3cff8f190f610a828314848b7c8280cddecd7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist.md", "original_path": "HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8547106f4e1d90acb7040b6d70851f8b0d00214522d599bcddf7038f3526fb31"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories.md", "original_path": "HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7dd010774a30f0ebb286c220f31582eceebba68eef01c4a57a5a586559b167c6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f4b7f7ac364907185f0ec5ece0364df73826743d5e4cc18bf682820fa06056fa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ae70f7b5047965bbcef5be7b388caa4c9406514885cf1beb19b19955489820f1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bf33f6f0ec1a0935716dfb2e9526850eb760c15b99e38729b16ea3272054c155"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "21d7f7a864795ad38737b9e21939807eb91c601987d09030d74a520eed650400"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "614b60c9262ff93aa22a5797c5f15dd51e141feb5e4a6da26caed785c79189fa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cf585795ae5e45f435d474c823829dc44091d82807fde33c0d58935e9c743d7b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9e3bd18bd34e150ac989e06e72d0f58a0a42b79e18a2e3b21ee5619b25b54094"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5f4b10329f98816164b955bba8d5da791f9467e8ca8739bdaf98ac216745f0cb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e48b68b98d07f1f0b9b9ea7a08e5927ec53823fc076fa2b61949ac48fcc9fb0d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ecd56f37e25ba12fa770a968e18e1f23cbc7a49dda5ebd8f7296b23b7d305df9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06.md", "original_path": "HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cf22ad67498321b080839c897345d08777aa431c987579f80ed18682320e7754"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/HomeDevicesQoD/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/HomeDevicesQoD/documentation/SupportingDocuments/README.MD", "original_path": "HomeDevicesQoD/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bc9eed7df13c8b7518889eea74a9ea7996fa409a6540f837f40338175f9f105a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/InHomeDeviceManagement/README/raw.md", "normalized_path": "original/InHomeDeviceManagement/README.md", "original_path": "InHomeDeviceManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "447fe1d66fee128a4b32c9f5c3d416129cae1002630e3b42f953797202e90430"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/InHomeDeviceManagement/code/API_definitions/README/raw.md", "normalized_path": "original/InHomeDeviceManagement/code/API_definitions/README.MD", "original_path": "InHomeDeviceManagement/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/InHomeDeviceManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/InHomeDeviceManagement/documentation/API_documentation/README.MD", "original_path": "InHomeDeviceManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/InHomeDeviceManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/InHomeDeviceManagement/documentation/SupportingDocuments/README.MD", "original_path": "InHomeDeviceManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTDeviceManagement/README/raw.md", "normalized_path": "original/IoTDeviceManagement/README.md", "original_path": "IoTDeviceManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "91bcf65732df9193d07fdb3261d713dbf259f7a0b47d2a9ef4db5a12706da97f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTDeviceManagement/code/API_definitions/README/raw.md", "normalized_path": "original/IoTDeviceManagement/code/API_definitions/README.MD", "original_path": "IoTDeviceManagement/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTDeviceManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/IoTDeviceManagement/documentation/API_documentation/README.MD", "original_path": "IoTDeviceManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTDeviceManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/IoTDeviceManagement/documentation/SupportingDocuments/README.MD", "original_path": "IoTDeviceManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/README/raw.md", "normalized_path": "original/IoTNetworkOptimization/README.md", "original_path": "IoTNetworkOptimization/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "465e63328c8dd3cbbed9a5419f4ea40533b89c26866450281601d7937a2001c1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/code/API_definitions/README/raw.md", "normalized_path": "original/IoTNetworkOptimization/code/API_definitions/README.MD", "original_path": "IoTNetworkOptimization/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/IoTNetworkOptimization/code/API_definitions/iot-network-optimization/raw.md", "normalized_path": "original/IoTNetworkOptimization/code/API_definitions/iot-network-optimization.yaml", "original_path": "IoTNetworkOptimization/code/API_definitions/iot-network-optimization.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c50aa4cb69a1d40cf97d801b1b4862a295986cf2eb11fe612bc8c2744b3b0ec0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1/raw.md", "normalized_path": "original/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1.md", "original_path": "IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0779199774e36195dd20cd4ef5301bba0713581c3db89325a497f9f8e5684b21"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/documentation/API_documentation/README/raw.md", "normalized_path": "original/IoTNetworkOptimization/documentation/API_documentation/README.MD", "original_path": "IoTNetworkOptimization/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist/raw.md", "normalized_path": "original/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist.md", "original_path": "IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f01c916458509e7096cab8be1dc081cd8827022cd50d03129edbd65987c5ee00"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTNetworkOptimization/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/IoTNetworkOptimization/documentation/SupportingDocuments/README.MD", "original_path": "IoTNetworkOptimization/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/README/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/README.md", "original_path": "IoTSIMFraudPrevention/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "549a14fbff7c4fce4bdce4a58728cdd35fcdc9fd385652fc7f352e3f6964c4f2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/code/API_definitions/README/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/code/API_definitions/README.MD", "original_path": "IoTSIMFraudPrevention/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions.yaml", "original_path": "IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b4ce9fa3c89118f85ffd4f7b2257f313021c5052a9ed3d4853f37252fd5615eb"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention.yaml", "original_path": "IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2acd3e3b2876ffa5e9824321935728cb5eff7dbbfe5d54973ba29b41bd65983a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/documentation/API_documentation/README/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/documentation/API_documentation/README.MD", "original_path": "IoTSIMFraudPrevention/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md", "original_path": "IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cd40589f6d5100ff000374d06589921bf9b2a4b0b6cb4819765b2e0d81c0d7c4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist.md", "original_path": "IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "93af68fc7993ccbd5b6d370ff5adb399870738ddf418b277a39a8e9abed9f3ae"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/IoTSIMFraudPrevention/documentation/SupportingDocuments/README.MD", "original_path": "IoTSIMFraudPrevention/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/README/raw.md", "normalized_path": "original/KnowYourCustomer/README.md", "original_path": "KnowYourCustomer/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "84602b50ce4cdaa990f9ad8a8672c84081f3e3e9412d320abc39baedd2ceb552"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomer/code/API_definitions/kyc-age-verification/raw.md", "normalized_path": "original/KnowYourCustomer/code/API_definitions/kyc-age-verification.yaml", "original_path": "KnowYourCustomer/code/API_definitions/kyc-age-verification.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f122880b1585408ce82fa73de81800cd1c065e6a7257367dd04839253158257f"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomer/code/API_definitions/kyc-fill-in/raw.md", "normalized_path": "original/KnowYourCustomer/code/API_definitions/kyc-fill-in.yaml", "original_path": "KnowYourCustomer/code/API_definitions/kyc-fill-in.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2d1705edc43e58bbbea1f17c65afbfcd91880d6611dd9f8c8c261b6f25e0ef99"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomer/code/API_definitions/kyc-match/raw.md", "normalized_path": "original/KnowYourCustomer/code/API_definitions/kyc-match.yaml", "original_path": "KnowYourCustomer/code/API_definitions/kyc-match.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a586c7880007856ba098d1ca0c568daf8aa7673d131b0e8e43848351de5f20fa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in.md", "original_path": "KnowYourCustomer/documentation/API_documentation/KYC-Fill-in.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "48baa2678450480f626ec86b53033052f480bb66786b4d266940adccc6421acf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/KYC-Match/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/KYC-Match.md", "original_path": "KnowYourCustomer/documentation/API_documentation/KYC-Match.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cd36af440f8a5b027d8615deb9c7996d771d9c3ed3461d9998f73a1f753ba977"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story.md", "original_path": "KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c8d22cdee923e538d015362287b8325af161abee47610dc27c9104d3e2ceb2ee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md", "original_path": "KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "87ae7ba07b4c54a474a4f3b78108e8bbdaa76c42d20706b76927466c824a53c6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md", "original_path": "KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1f930139665d3997dd33fe4bcb2c03d6a5221bb0d2f4f18da6f9ab882c037809"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md", "original_path": "KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "81862106f15b4b8bae268600e9860ac1ba2e725f9e97d312a22e03eca83e2aa1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f0240fe90e8962930ffd539c856a7993d703493b1e6f8597658bf4728906c341"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "58e8d6ebb5d8d71e524b16eba12fb47c448aa165a0258c8fa41ab86d9d358558"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "70866beb872728179e8dd5b8d463aa05dcc0ecd63786647e33a9a1df1f4e2b23"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ab8acc7b573e67be4251f71cb4497b28b724d927ab3f586ecffda69d13b46639"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "dfb5ad84e3f394676bb7b7fe7dae861ab83ea84168c88737c83c68cdb70da845"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8fffc9ba5311b09e830e847aa24226a1cc53a3b39e41d10fd500e6780b97547f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f0d91e1901433fd9939f5eb9d6f7934389f8cb152a61b3ea5fec70554aa74fc4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fcbc0ab0f0127af723c05986748532d1a7fcb930abc7903cf18a9fc6fee58f00"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "59dd31da64d72c08cd9d07356bd7a69f3414201eb0743fd8f597c727a5b6e045"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9ac3c1d71569c45b660b08b0db513ef24274be4b5e328065bf88fe10b0ca8673"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a92e47733171b85cbccadd68217f3389fae83ae7efd6247e307f58594695f682"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "747656bf065d73e044a7ce086d08b8bbf9cff9e432c16c4dfa728f088e9273c2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fe38de2364eb586de5509db96328c1c36a027c1bbbfcb703f19dc3abdfdb5416"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "66a7bdafca087c84e83bd29d9fecdcddf643144cfaaf422803b922eea0efb606"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f069090603d208e306d67b9a46dac6dc66967071d0f065766c8a37b8d7f90548"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "703cc0e38c5d1305aadbe5c5aaea1027a381d83cc562084f2a6348f9020c42d4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5c30170966e268ad5210a2942d5dd40cce313e17ad09d6948dca765e8e8ee6fc"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "97595e7cc4ad2ef41eb1bebcaf9ff01f9c8c5ab4f6e2c70625aaf1f8aee1250c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "490e66d5a8cb909f7d72ad61620f23e56a9b0da2aa5ff804fce4d58dbdda19fe"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "df66878a3073802e97708b4e4637a4d2e4a5f452658768af0ea1fcfa581c8965"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20.md", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "27fcb723f30b5c78c82c945ae16add8fc7f3db605e9c9cced0899940493ff113"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomer/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/KnowYourCustomer/documentation/MeetingMinutes/README.MD", "original_path": "KnowYourCustomer/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerAgeVerification/README/raw.md", "normalized_path": "original/KnowYourCustomerAgeVerification/README.md", "original_path": "KnowYourCustomerAgeVerification/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9d5cc92c5e11bf90af2dde3a9672dbc07c00904adc5ef44c4fd710cf94aea5a9"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification/raw.md", "normalized_path": "original/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification.yaml", "original_path": "KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "23b8ecc5c7f23ca6229e98ebbdc6615919cbebbd78048d8544c32efcfc7a903c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md", "original_path": "KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "56f3e75682e94d185693f8275a848d434d4da724455bbf18e26ae59b71b0cef8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story/raw.md", "normalized_path": "original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story.md", "original_path": "KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "375a7bb6929fd1cd0cb6fe489bc28f88668bd20a268d354a86594652ee13664e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README.MD", "original_path": "KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/README/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/README.md", "original_path": "KnowYourCustomerFill-in/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e10091ca2f2fae417eea01e2f523c5eb5f0bb9bcdc16f2e887190d23c32d3154"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/code/API_definitions/README/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/code/API_definitions/README.MD", "original_path": "KnowYourCustomerFill-in/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in.yaml", "original_path": "KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "123188d0d26b8f0dfd53201ce1426d92e5ffe941d720a1e9b80f8a459dac7364"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story.md", "original_path": "KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c8d22cdee923e538d015362287b8325af161abee47610dc27c9104d3e2ceb2ee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/documentation/API_documentation/README/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/documentation/API_documentation/README.MD", "original_path": "KnowYourCustomerFill-in/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md", "original_path": "KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "aab412696ab8558196fca3bc61f117e8278177a7a84afa0743f697ea94a5a524"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerFill-in/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/KnowYourCustomerFill-in/documentation/SupportingDocuments/README.MD", "original_path": "KnowYourCustomerFill-in/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/README/raw.md", "normalized_path": "original/KnowYourCustomerMatch/README.md", "original_path": "KnowYourCustomerMatch/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "06ade2bb3ee72f98167b7fef2e075d201a78f4630327ae0d3ac0ea6e3f41e720"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/code/API_definitions/README/raw.md", "normalized_path": "original/KnowYourCustomerMatch/code/API_definitions/README.MD", "original_path": "KnowYourCustomerMatch/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/KnowYourCustomerMatch/code/API_definitions/kyc-match/raw.md", "normalized_path": "original/KnowYourCustomerMatch/code/API_definitions/kyc-match.yaml", "original_path": "KnowYourCustomerMatch/code/API_definitions/kyc-match.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "39c53021a1afef48ba9b0c1b81747148edf6f3b7c3df349b99cb4db7ca226b97"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md", "normalized_path": "original/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story.md", "original_path": "KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c8d22cdee923e538d015362287b8325af161abee47610dc27c9104d3e2ceb2ee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/documentation/API_documentation/README/raw.md", "normalized_path": "original/KnowYourCustomerMatch/documentation/API_documentation/README.MD", "original_path": "KnowYourCustomerMatch/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md", "normalized_path": "original/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md", "original_path": "KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "70f4266872bc813572a8b4dd6825d6ec9ef9b57ccabe898cd76f6b5be5f91fad"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/KnowYourCustomerMatch/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/KnowYourCustomerMatch/documentation/SupportingDocuments/README.MD", "original_path": "KnowYourCustomerMatch/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/README/raw.md", "normalized_path": "original/ModelAsAService/README.md", "original_path": "ModelAsAService/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e382b3c23cb054ac9842c0fa3d3cd82995f16cc897c455ffb91a40f69b3b43a4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/code/API_definitions/README/raw.md", "normalized_path": "original/ModelAsAService/code/API_definitions/README.MD", "original_path": "ModelAsAService/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ModelAsAService/code/API_definitions/knowledge-base/raw.md", "normalized_path": "original/ModelAsAService/code/API_definitions/knowledge-base.yaml", "original_path": "ModelAsAService/code/API_definitions/knowledge-base.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "91a724ef5f9a38d1e827ee09bb46801706df94fe047f00497b6bfc0a66af68e3"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ModelAsAService/code/API_definitions/qa-assistant-manage/raw.md", "normalized_path": "original/ModelAsAService/code/API_definitions/qa-assistant-manage.yaml", "original_path": "ModelAsAService/code/API_definitions/qa-assistant-manage.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c4de6ddd53bb0fcb092e8430592315b2ccc7b1d08ad876af4aa415e2b3118c5c"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ModelAsAService/code/API_definitions/qa-assistant-service/raw.md", "normalized_path": "original/ModelAsAService/code/API_definitions/qa-assistant-service.yaml", "original_path": "ModelAsAService/code/API_definitions/qa-assistant-service.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b2f607d546552809244076de61fcefd0eefcd1418a26ac5495c3d81a1cc7aa87"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md", "original_path": "ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "13cd1fc8ea2d9c4a6523dec6d2dfd4fb871d72fad897c7a27120adcf149bc2d4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md", "original_path": "ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3cdfc9da5eefc48754be894efd9d57fd706ca0ffc38bfd88223c34284b46458f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md", "original_path": "ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "88bed02f2e2ad993f7d2e2dacbba9c75dd8175e9d070b21b03da0be4b38f1c4b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md", "original_path": "ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "20cd296f1cad3a7511c708b471f3b6ebaed5e9f593f141bd44db3ab3311d983e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/README/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/README.MD", "original_path": "ModelAsAService/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist.md", "original_path": "ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "53aaa8673f479e4b42ec2776482607802ca055843e8c894af50e861674fd70d8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist.md", "original_path": "ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "465cad5d57d4d3fb2d99a96d36e9de84698a6ce71362d3a66dbff37f25dbd2cd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist/raw.md", "normalized_path": "original/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist.md", "original_path": "ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d7fcfb3126cf9d01df7d3d52696a4f17b0ff14c4440e3e584d434c90f0d49d60"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ModelAsAService/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ModelAsAService/documentation/SupportingDocuments/README.MD", "original_path": "ModelAsAService/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MostFrequentLocation/README/raw.md", "normalized_path": "original/MostFrequentLocation/README.md", "original_path": "MostFrequentLocation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "679ccabd4e22331f467fd62b12d1a19e2ed52692f37d775e9c6f327c7759086e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/MostFrequentLocation/code/API_definitions/most-frequent-location/raw.md", "normalized_path": "original/MostFrequentLocation/code/API_definitions/most-frequent-location.yaml", "original_path": "MostFrequentLocation/code/API_definitions/most-frequent-location.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d13221887a6081eae251a84c4d5bb07474e6270b539aafb00ab9ff924bdc875f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist/raw.md", "normalized_path": "original/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist.md", "original_path": "MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4936d1898babeb01879600bae0d117cba9b9d1a715e1b87d75b8a362d687d696"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations/raw.md", "normalized_path": "original/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations.md", "original_path": "MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b19f3dd24b2fdbdc974511ebd0c23a46de634e203ce43687579a8f4380480c6f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MultiPointVPN/README/raw.md", "normalized_path": "original/MultiPointVPN/README.md", "original_path": "MultiPointVPN/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d7d78f4d1e5255cec78488740a769de7a2cfca56d7f97a71ef13d60be9f94770"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MultiPointVPN/code/API_definitions/README/raw.md", "normalized_path": "original/MultiPointVPN/code/API_definitions/README.MD", "original_path": "MultiPointVPN/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/MultiPointVPN/code/API_definitions/multi-point-vpn/raw.md", "normalized_path": "original/MultiPointVPN/code/API_definitions/multi-point-vpn.yaml", "original_path": "MultiPointVPN/code/API_definitions/multi-point-vpn.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0a4a584664b506794b19555e89eb1e3bc907adefa7f69e41eb164d924966dc73"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MultiPointVPN/documentation/API_documentation/README/raw.md", "normalized_path": "original/MultiPointVPN/documentation/API_documentation/README.MD", "original_path": "MultiPointVPN/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/MultiPointVPN/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/MultiPointVPN/documentation/SupportingDocuments/README.MD", "original_path": "MultiPointVPN/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/README/raw.md", "normalized_path": "original/NetworkAccessManagement/README.md", "original_path": "NetworkAccessManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9afbd862cac1ae7de989b71dd7638b31dada81ce5b75f138451b1d9d8fd1c5e4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/README/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/README.md", "original_path": "NetworkAccessManagement/code/API_definitions/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b5f07cf359a8e9ef7719e715c35deaaded8136b76c22d85c875ad0444f19491f"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/common/CAMARA_common/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/common/CAMARA_common.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/common/CAMARA_common.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2326ffea965da04cf88bc59e1875189e5b8ca52a940b64038b864fd877ed9a6a"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/AccessDetail/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/AccessDetail.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/AccessDetail.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "afb73c5d3aa091452bbe62db86ed46494d922bd3d9b0c66c8814a197f41eda9c"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/NAM_Common/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/NAM_Common.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/NAM_Common.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c38112ca704b2ae2f9a5fca94153591232ca5dd3efe38eef06b998da347c644a"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/NetworkAccessDevices/NetworkAccessDevices/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/NetworkAccessDevices/NetworkAccessDevices.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/NetworkAccessDevices/NetworkAccessDevices.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e607176137d90ecf1df86ab8151ebd4555f39efd0d1efef0b9213e766bba3bda"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/Policy/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/Policy.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/Policy.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8bc140e444f9b4951026a5b49e92a2096bb188a55c7e3b2a58ca7b228980f9fb"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/RebootRequests/RebootRequests/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/RebootRequests/RebootRequests.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/RebootRequests/RebootRequests.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ccdc0071c276d8c7fae495ab80c944e1a5c7919a0134356fed8ebe40ea48c450"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3c514395211f4f438d4204dc2cedada1c4ceb573c38bd8fd67ef0024d82b1478"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/Services/Services/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/Services/Services.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/Services/Services.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3ef57527c7cb255717e66ab4587d565631e71ac5fcc6c838401f72a89d3de0e8"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "829accbba205ca4b077e94f614649ca8b522ee462b6128e8a5fc761d9a8c0f69"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a14ba91d856fbaf51dec8630d129b2a1102c96ec9daf9f14099f26bf822d3387"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/network-access-management/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/network-access-management.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/network-access-management.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "032905db97db20a06c55f41cb6de46bbe0cf2a48a171ce20714a9d1bc36ca72d"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkAccessManagement/code/API_definitions/redocly/raw.md", "normalized_path": "original/NetworkAccessManagement/code/API_definitions/redocly.yaml", "original_path": "NetworkAccessManagement/code/API_definitions/redocly.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6ebf13ec4a7150853bf28539578fbaab7aeeb0b67643cb7d8a04119ff24924c5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story/raw.md", "normalized_path": "original/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story.md", "original_path": "NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "97a83c0eb8b509616ff694319517b64a9366f2eff9cbe39c32754ae68a026cf8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/NetworkAccessManagement/documentation/API_documentation/README.MD", "original_path": "NetworkAccessManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b0e86e9bc6e2e74be205fae8574595f9eb5128e371260ac666378cf1bd76d313"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story/raw.md", "normalized_path": "original/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story.md", "original_path": "NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fea3ad365c6d4b62c376e867cdd30728894e47119984b4b3579f0764d8ce1f1d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist/raw.md", "normalized_path": "original/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist.md", "original_path": "NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4c5ee192cc5e5e94efeec0e7a32392b594872851cd0e65de0556aeb0b45493d8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkAccessManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/NetworkAccessManagement/documentation/SupportingDocuments/README.MD", "original_path": "NetworkAccessManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkInsights/README/raw.md", "normalized_path": "original/NetworkInsights/README.md", "original_path": "NetworkInsights/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "30f51babba6b8aea1043195cfb3db41d10ba004fe45fd201c7da2018da032fee"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkInsights/code/API_definitions/network-health-assessment/raw.md", "normalized_path": "original/NetworkInsights/code/API_definitions/network-health-assessment.yaml", "original_path": "NetworkInsights/code/API_definitions/network-health-assessment.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e050b9ae07d4c59f29ce543b1971655b96e31949376a6a81fdbc2bb6a62baa32"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkInsights/code/API_definitions/network-traffic-analysis/raw.md", "normalized_path": "original/NetworkInsights/code/API_definitions/network-traffic-analysis.yaml", "original_path": "NetworkInsights/code/API_definitions/network-traffic-analysis.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3944f41cd90f709fb02d410e909524486d5ae808d620dc2087e148846e3c193d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkInsights/documentation/API_documentation/NHA_User_Story/raw.md", "normalized_path": "original/NetworkInsights/documentation/API_documentation/NHA_User_Story.md", "original_path": "NetworkInsights/documentation/API_documentation/NHA_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4bd9f17329fee47692635efd8a4e03c2f7164bcd22ae1753da604f2079d9246a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkInsights/documentation/API_documentation/NTA_User_Story/raw.md", "normalized_path": "original/NetworkInsights/documentation/API_documentation/NTA_User_Story.md", "original_path": "NetworkInsights/documentation/API_documentation/NTA_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c906b809e5079387dd1ef539b759b2b084d4d4d5789247bcf6ba88f81cd3cd51"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkInsights/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/NetworkInsights/documentation/SupportingDocuments/README.MD", "original_path": "NetworkInsights/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/README/raw.md", "normalized_path": "original/NetworkSliceBooking/README.md", "original_path": "NetworkSliceBooking/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5ac2f569bbca0e0be5e5c6e16ea78f58fc692a7e662ee01037566da769c4d2c1"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkSliceBooking/code/API_definitions/network-slice-assignment/raw.md", "normalized_path": "original/NetworkSliceBooking/code/API_definitions/network-slice-assignment.yaml", "original_path": "NetworkSliceBooking/code/API_definitions/network-slice-assignment.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "947ad1b2890a4a39c7bb3ce82ae1fc02f3d18c4c301317ba620425b4d3c25f8e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NetworkSliceBooking/code/API_definitions/network-slice-booking/raw.md", "normalized_path": "original/NetworkSliceBooking/code/API_definitions/network-slice-booking.yaml", "original_path": "NetworkSliceBooking/code/API_definitions/network-slice-booking.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "efa744456e5e50de32c357f8efe7edab258c8633e37bdd4b4fe15899ccac83b1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "22b457f8e48784ad647e7c0d294bc92e9b7ce7e3dc3d55e6ac0a6b2f89efccee"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/NSA_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c2fd64b1f568c14ee2fa9f9cef9aa38d054a259202668318291721f73127c51f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/NSB_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fa05a7db8d28949d1928ba5e0fe2ce4059f66bd3fb1ac19e101db1ecd6f46490"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1c18633da918b5c46e58e649edb20fda44f7393cbe945bd9849d06bbac9fbb1c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55e7f531498546c96f512ea8b2839b9418416d98efc9d9991e7f49bc905585db"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist.md", "original_path": "NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2997de2de4625745ae643b95affa34bb906148beac380208000bb22a6579e344"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "05114c4061bb7cc9ec0e178cf0a282e908335d8b54758c7f4b22b3019d4b8a65"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8452e4b7aa6aaac87087fddb9e0e4f79a6e73333d18dd8c83b2ac3357ccb5a60"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c057982de7a5f84f7a73d0e77d817e5f6df2f3799b2ed783610528d9fdf27355"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c057982de7a5f84f7a73d0e77d817e5f6df2f3799b2ed783610528d9fdf27355"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c239127619503c9f8b5464461990a0a8d5d293034a6b768f0d660c20cb82785d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ddcb4646d46260321f4f964b1860e79eeb0bdb01d2fa12e21c4cc83c28e40ec9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "52ce284fe220f57b5fcb927511524c36b582e42b7155620a9164999c8a45807a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "650a0e2128e49362119de71b1876779441eccb479862b024bda821eee47c9d9a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e9980b1c8c29ec8c03975b08731042f0d88cfe3e0cff063b575a3bd8ec107164"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26/raw.md", "normalized_path": "original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26.md", "original_path": "NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c7fc2b8aff7f32ca3a5e84b4db127d9c05e53ef4a691ba5f5ba7acda0e830ef2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberRecycling/README/raw.md", "normalized_path": "original/NumberRecycling/README.md", "original_path": "NumberRecycling/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "72de98a2afe9ed1930737419fc0df6f3bab95f2f1c515a8c14866f27f0f418d2"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NumberRecycling/code/API_definitions/number-recycling/raw.md", "normalized_path": "original/NumberRecycling/code/API_definitions/number-recycling.yaml", "original_path": "NumberRecycling/code/API_definitions/number-recycling.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0d483eb77700064812d8430a18fcdb79d541392625725362a372c49f513d2232"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story/raw.md", "normalized_path": "original/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story.md", "original_path": "NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "983e2d13a4e87849ab3ebb3ca55aa7c5c0cda68916fe4090774bdc888064997d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist/raw.md", "normalized_path": "original/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist.md", "original_path": "NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "30ba6d61eca358bae091093d969ff153836c738546d690d60e1296aa0bd53640"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberRecycling/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/NumberRecycling/documentation/SupportingDocuments/README.MD", "original_path": "NumberRecycling/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/README/raw.md", "normalized_path": "original/NumberVerification/README.md", "original_path": "NumberVerification/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e7361baad6c238d513c941d71367951c2960fb88c7d9d8c96a25f8589f747488"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/NumberVerification/code/API_definitions/number-verification/raw.md", "normalized_path": "original/NumberVerification/code/API_definitions/number-verification.yaml", "original_path": "NumberVerification/code/API_definitions/number-verification.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b07a959f11f941da03ce86e506510cd9103d93f7fcc0334bdfd6b840bf2b7bda"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story/raw.md", "normalized_path": "original/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md", "original_path": "NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "26e2de25ad198bc95d39fae1ba36c97d99d14815ddd7f17e41c540d4c2512ada"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story/raw.md", "normalized_path": "original/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story.md", "original_path": "NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "82902c98109afa0a14cd0d751461ee38fc98ae95381a9ff3cbd5c2490867222c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist/raw.md", "normalized_path": "original/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist.md", "original_path": "NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "059e8c18474bfb1236d902fa0e3dacf8e08a97db728f0c9e2db5474824502afe"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e79a4b6f1a0212147c34ec9e10ef8956cd14f55d757d87224d9853a4acd2a501"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b2f7c5f40fa6524aef9b2a969c2dc5ad74e33fc5e0bc8e855322c8b8e674aca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9a770b17220479eeb29d1c6a51d606bfa31f5a566138456480d39c68fcee6729"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "45bb46795bf6f30bfdf18dfafa9fe3b759bf673fdadcf1ae00387bbeb36b1b5e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "90ec1f57173f4de79c2d8cb9ad9a12d593414d035029c03ac41e0a91ec49ce82"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0a441b0a12a43bd55a25abd7c475b10d467974bfed9f7cd0a30e694917f5e24a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "755ff706563367c4f3d8dd2b599b71a77b78570f4ad0d5f39a2a0632698a02ad"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "957a8b8bcc9cad6b08a81ad2e3e698ee6d916be0601c58b09223418193daa6f6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "06e275cc0cdd3c674af3a230d3e890ba3d5227b5ae5b2f7aa5b1efab2dc67f06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "97e1b9f14e7835571c206ba8c75525d7dabea5ebd91cb234c015c8595b753b12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "345d88996323221d9c826e25c9fa5d731adeb8f6fc039fe0228b11da2744eee8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4e7ffa21ec92d90ef15ba2f77f0611e6eeabbda19f66a669d2e11c63622b49f5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "baa7c13ce0f25641cd84fa87a9fef7ac7e6c3373869c4bc8b857b0731c7dd538"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d11953ae35553c9f8d4b6e831820d80db787e3a873ff48c3d79d18ed51c2faf1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cbc470b467fae54d2b89e29f3561f82689fc29f6f220e8abd337feae211aa543"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "29a64990b9f722b2b683e36fe3a44b7bbd5ffcd74120bad550f983bfbe27ed06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d8bcbfbc47707b7c43f4ccf5ba7b98b7054265a8530238bb090b6c588e3cbe12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0e9e878aaa9c9fc15659e94ca2eb633018ed3d7dc42c88a039fe15c31bd24eda"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "original_path": "NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c17e36ff01a917e24a55ce18e45ac2b831eccac545ffed4afde5afea595aa7b4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/NumberVerification/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/NumberVerification/documentation/MeetingMinutes/README.MD", "original_path": "NumberVerification/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d2db7da49feec8cb4a4546aaba1278db2685b1881e37d311d977644d2ed5dc64"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/README/raw.md", "normalized_path": "original/OTPValidation/README.md", "original_path": "OTPValidation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "12f7ddf90d480b4937f4d289ccdbb2d7779a187a3d74f2f91dde380856087676"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/OTPValidation/code/API_definitions/one-time-password-sms/raw.md", "normalized_path": "original/OTPValidation/code/API_definitions/one-time-password-sms.yaml", "original_path": "OTPValidation/code/API_definitions/one-time-password-sms.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fd66461e8574271cc93f6f87f568d3816b6994e44b11398d464d1919100b2af4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story/raw.md", "normalized_path": "original/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story.md", "original_path": "OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1475a2a17d434a5863bf545a194697d95aba053e2e0be911f5506483b2994ee8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/API_documentation/OTP_SMS_API/raw.md", "normalized_path": "original/OTPValidation/documentation/API_documentation/OTP_SMS_API.md", "original_path": "OTPValidation/documentation/API_documentation/OTP_SMS_API.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9645eb62e3ae723975d9751028ae410904a397e5f78606abddb4196e9457fdad"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist/raw.md", "normalized_path": "original/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist.md", "original_path": "OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2229f3cc2e7cf33995a61c46e0353f11629222284e6e9bd4702f563c184888c0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e79a4b6f1a0212147c34ec9e10ef8956cd14f55d757d87224d9853a4acd2a501"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b2f7c5f40fa6524aef9b2a969c2dc5ad74e33fc5e0bc8e855322c8b8e674aca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "81c81846ec0b1eb669b5d5dbc32b70642e526b1208ca732a6fb056dae00dbc31"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "45bb46795bf6f30bfdf18dfafa9fe3b759bf673fdadcf1ae00387bbeb36b1b5e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "90ec1f57173f4de79c2d8cb9ad9a12d593414d035029c03ac41e0a91ec49ce82"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0a441b0a12a43bd55a25abd7c475b10d467974bfed9f7cd0a30e694917f5e24a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "755ff706563367c4f3d8dd2b599b71a77b78570f4ad0d5f39a2a0632698a02ad"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3f45fe1af4e55042b8f3218c314ce48f047c4e4d0d59bc5995837ea86cd888f1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "957a8b8bcc9cad6b08a81ad2e3e698ee6d916be0601c58b09223418193daa6f6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "06e275cc0cdd3c674af3a230d3e890ba3d5227b5ae5b2f7aa5b1efab2dc67f06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "97e1b9f14e7835571c206ba8c75525d7dabea5ebd91cb234c015c8595b753b12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "345d88996323221d9c826e25c9fa5d731adeb8f6fc039fe0228b11da2744eee8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9f7814882220d9785404ea086dff971d92023327a061c6b914e743e9f37a0192"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "baa7c13ce0f25641cd84fa87a9fef7ac7e6c3373869c4bc8b857b0731c7dd538"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d11953ae35553c9f8d4b6e831820d80db787e3a873ff48c3d79d18ed51c2faf1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cbc470b467fae54d2b89e29f3561f82689fc29f6f220e8abd337feae211aa543"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "29a64990b9f722b2b683e36fe3a44b7bbd5ffcd74120bad550f983bfbe27ed06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d8bcbfbc47707b7c43f4ccf5ba7b98b7054265a8530238bb090b6c588e3cbe12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3864f05898df8027b515face59c4ca9e708e579a09bb553c7fb3175bcae1f14b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "original_path": "OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c17e36ff01a917e24a55ce18e45ac2b831eccac545ffed4afde5afea595aa7b4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/OTPValidation/documentation/MeetingMinutes/README.MD", "original_path": "OTPValidation/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2480317ffd631ac3584a1378b76773e5c16a249fd117167544bb128c4ea6d143"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OTPValidation/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/OTPValidation/documentation/SupportingDocuments/README.MD", "original_path": "OTPValidation/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bc9eed7df13c8b7518889eea74a9ea7996fa409a6540f837f40338175f9f105a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/README/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/README.md", "original_path": "OptimalEdgeDiscovery/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "28c02ade0acdc4ad4f0c64dbfcd15ed51ad9b2ffe08a7e1da614467d7069835b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/code/API_definitions/README/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/code/API_definitions/README.MD", "original_path": "OptimalEdgeDiscovery/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery.yaml", "original_path": "OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a49e64df17925398939413995db082421a9c457ba6dc317c88f1ecff76849066"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/documentation/API_documentation/README/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/documentation/API_documentation/README.MD", "original_path": "OptimalEdgeDiscovery/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist.md", "original_path": "OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "878f2ab2c4b50cc6a9b5b62a54a7d09536d19b3ec1b2a0cf0a2c6b42761c26f0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story.md", "original_path": "OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5011071bf43bd8ad10f11d0691d57ca47806c64c03f9b15cac70d190ed265265"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/OptimalEdgeDiscovery/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/OptimalEdgeDiscovery/documentation/SupportingDocuments/README.MD", "original_path": "OptimalEdgeDiscovery/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/README/raw.md", "normalized_path": "original/PopulationDensityData/README.md", "original_path": "PopulationDensityData/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "35c95bd5120b7a3623d3e33c9ea5ba265d932549d3b2bb7ba980d440986706eb"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/PopulationDensityData/code/API_definitions/population-density-data/raw.md", "normalized_path": "original/PopulationDensityData/code/API_definitions/population-density-data.yaml", "original_path": "PopulationDensityData/code/API_definitions/population-density-data.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1ffad2df49e098a2cfdcadee689532dad9a0cda8e74833844577ebeb857474c2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist/raw.md", "normalized_path": "original/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist.md", "original_path": "PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "892ffd3b5cdfd7a9b5b690deb7c3a4958a688f5ad80320d41129e52ddb1ae9c6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02/raw.md", "normalized_path": "original/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02.md", "original_path": "PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "05754fffe7a2db2ebd270c56eb95b26a21f59a465a37dbb98ac59f9a456aaaf3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24/raw.md", "normalized_path": "original/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md", "original_path": "PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7029fa961312786e456124c92a0ff594a3ba5b21d44249e1320c546bdc3cea7f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/PopulationDensityData/documentation/MeetingMinutes/README.MD", "original_path": "PopulationDensityData/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal/raw.md", "normalized_path": "original/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal.md", "original_path": "PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d8dfa86358da04480d63764c023bf609b8203d4f44a438e72fb0bcb4432c14ed"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PopulationDensityData/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/PopulationDensityData/documentation/SupportingDocuments/README.MD", "original_path": "PopulationDensityData/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PredictiveConnectivityData/README/raw.md", "normalized_path": "original/PredictiveConnectivityData/README.md", "original_path": "PredictiveConnectivityData/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a1e62e434a272a2260e28e16eb0a7ab9c83273908123e0ca6f60ab09ac306825"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data/raw.md", "normalized_path": "original/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data.yaml", "original_path": "PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "51f7b71b1e30d435417f209031f82f2fab1845bd3c895ed62d3505f39ba34098"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story/raw.md", "normalized_path": "original/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.md", "original_path": "PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5aa11d5b5d5909743d43d160f75aa2f85c45746573a7120bc9cdffda71672c6d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist/raw.md", "normalized_path": "original/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist.md", "original_path": "PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b75f640291d37927f3d613eebbc11fd9dc9bf1a0446078e78f318520754a242f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QoSBooking/README/raw.md", "normalized_path": "original/QoSBooking/README.md", "original_path": "QoSBooking/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3647b5cc8180c62f6e3ca613f68c5e36de06891d76d8d76514e3a3d0c4bf63a7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/QoSBooking/code/API_definitions/qos-booking-and-assignment/raw.md", "normalized_path": "original/QoSBooking/code/API_definitions/qos-booking-and-assignment.yaml", "original_path": "QoSBooking/code/API_definitions/qos-booking-and-assignment.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "686308ae07e88327c75ec40b1400a4b3ee3478916813ffcfe96e536d714ea4e2"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/QoSBooking/code/API_definitions/qos-booking/raw.md", "normalized_path": "original/QoSBooking/code/API_definitions/qos-booking.yaml", "original_path": "QoSBooking/code/API_definitions/qos-booking.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1f69506512c9b7bd7690df5965f36000b2bd8f1540e2888a52acb0447db6154d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist/raw.md", "normalized_path": "original/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist.md", "original_path": "QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c89cf2f2900524286b319cea2336e5e47873b5a22bfb04bc0175ce9788789bc5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist/raw.md", "normalized_path": "original/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist.md", "original_path": "QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "daafa0bd6e062009f019b28a119d40d892dd03929260b02c924d49bbe0a3dfa2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QoSBooking/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/QoSBooking/documentation/SupportingDocuments/README.MD", "original_path": "QoSBooking/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/README/raw.md", "normalized_path": "original/QualityOnDemand/README.md", "original_path": "QualityOnDemand/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9b02b587a0b7b428c6d868ae4affaf1eabf842c0086882cb503b7db052b1a099"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/QualityOnDemand/code/API_definitions/qos-profiles/raw.md", "normalized_path": "original/QualityOnDemand/code/API_definitions/qos-profiles.yaml", "original_path": "QualityOnDemand/code/API_definitions/qos-profiles.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "04674253679a15398680d32b6b95eba395d24642ae1f912871c342f2f49d8c42"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/QualityOnDemand/code/API_definitions/qos-provisioning/raw.md", "normalized_path": "original/QualityOnDemand/code/API_definitions/qos-provisioning.yaml", "original_path": "QualityOnDemand/code/API_definitions/qos-provisioning.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6ce713cf4c943b013f2eff7c04a76fe7bf8cef869d64ab8423131eb234123dba"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/QualityOnDemand/code/API_definitions/quality-on-demand/raw.md", "normalized_path": "original/QualityOnDemand/code/API_definitions/quality-on-demand.yaml", "original_path": "QualityOnDemand/code/API_definitions/quality-on-demand.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "35095de6c7d8ba8b7f35f7cc8a327eb06388d8455453e2d56b28c028ca24d2e2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/QoD_User_Story/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/QoD_User_Story.md", "original_path": "QualityOnDemand/documentation/API_documentation/QoD_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0593dbdf3d979b0ca6d0f4de53d40d8d41b34d585c56510fdb29432fd8d9ce54"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table.md", "original_path": "QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c81a411a9e130795877da11590aaf32807cc25cf1db36ff1c6048b97c33935ed"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story.md", "original_path": "QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8aac2cfbe90e968466fe888848210bb91bd39deb32b62b5190903e9fdc5591a8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist.md", "original_path": "QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0b0815484c8f0fbbb36dd7a7413f57c5fd12c72af6a56acae373274ff0dc3fb6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist.md", "original_path": "QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5ae8716de233f83a57cf6ce0d06a3a2aa3802a88f2df75b30494c886b02ea59f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist/raw.md", "normalized_path": "original/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist.md", "original_path": "QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b46858e297b2ece63375f76873e721a220e459bb6460b1d38100b937e316f5b7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f133cd04abae69f39ce577ebe3ac3d5855671d6cd8f6af0e6853d332d69ae458"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "fe6968f109f018c6d70c26ed7a86b17835836df484c9ed5f40d84e04cb05eca1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c16ec949b73ad20b0f41dbc37f978da9b767840bbabf4085a42eed6fe4476d05"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d1b97f83459fd37d8f364993d2d295d6758805fd523188522826f50eca4a8da2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ad556d7844c8e6f7f47d4975c426741f3ff76541574b9935291f6c9d8a912944"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "edd296d3597ae63a0b746110c8547a766aec860c3a7cf8b082f6bd362c4d9ee9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5b2ad95c0d21755a77954fc0eee9430ce2e799118db70c0d67b697810db3a0e0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "34aff778714b5e94afdbd1bb42a22d7c2a225a7fd3a81f62f6264fa4df3f3bbd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "de99a7d46a5968fab68e9408a102f5fd94cb9a18e1034726f791a7adef80e87c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7addd7e28af19e4d1353e8814855aaeba6a9b8c05e4e082948462f6be76b8ed0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1aebe7c9036a90cea83c3f52740172e953178999fd217a0814520e64f168de84"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e0bdc62eef22b65d2f75260fc3ea42d47254a480c487d067661f9536c2eb5a95"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3bbc1533a4cd9acb1d770c5a5c699c548fefc859c18d5a780c83cf3d64fcb80c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "12f5cd35f09ebeeeceffcdc8b10bbf89cc49c40858a0abec8f11b06b256fa923"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "54b260aed7188d4b5a4ba806a1b9397505dd67eac97cc67ebf38efaf7bccfcc9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6e71083c8d3a3562a759687d51a0cc8d904d6a4bcbe6b87262a9850f43cb4b2a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55cc29cc5bbfd10fcef73ae9722435867398e11c427ada37f18048c4adface3a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0418f99b11a399f81e97e15854f663f3d8436bfb1c56773f80c2b7a278bf285d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7aaf8b70db420735fa4586f8ef26c88b5a2cb2a1d46d6c4a5a73427e9b65fcd1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d5361b5aae23583181864ab1ad4d3e6aec435b0e25b660f97c2ff38f9f32ef18"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8f92983a64875f4de384bbb9ce6695d525bed654386665e2565083c61436f108"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a641a7781b495e3afce821cd0e1fa3bd0978beb404758a27e2b929a5ed70b176"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "490883bfe371bbf7a0a2e97bdc4efcbe23d98343495cfdae5e7fd827f57c080b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "40dd441b49287332f4d3346b280cbfe1dca2b86ac0cafe9e1eaabca0c06a2a1c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b09e6f47d67a2d9582c997b0cf81f1fa99e928b63284060a333fdc37cd290633"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c5a98c5b550e5c4ace3d9e754fadad19058fe92dcf50f598200feaf4ea2ffbb2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0463c692d3774daebab401ca412b413c4f06748c154652e54fd150d2474aae99"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "15093b20c61fc65d36710c10d5160bf9d2e30c9caf17b9f664367ac875298e6e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f11cd2c803bee556e2bf2d25a8599e5839accec03aa87f0d08e9612c2259dc3f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4631f35cfdebb0de48e2a0b133be4693d55f28a268bf826ce8ca325814a88541"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0289693bffa886aee561763d42a835d46044d748ddd954f94ef10a1b70dd2b88"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "606544a5663ce7d74a414477a5842f8a990dfc146cb890dca134c97350a26eb2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c9339a0895559ba23b5381accf2f211bfc63bb4d59d36f263b3dc93eef87f243"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "81ecf9a705ddd2f906fc1a917736f0b71cef5f488f507a23b498c0a95d111ccf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9b86e0865dcc8b23c55b23f804e22a0b3eb9b03b239b7b7540cee3d833c6d8a9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f267475d747e30ee4a19ca6e38ac9fe4d8f1ff93b7632c5151c8897510a75b3a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6ef8296cc6ec9c6784d3f391a61a9b686d273d1d8ebc60a057e7898a4b156675"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ad4d02f34dc24c2f9372cdc9cd92d18b8b682e229884e6d42219f909a02e2d9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c4c062a92df214f8fcb306d6c88b4d68fe88a111b99ab0d5608282a8e440691a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c8b47e42c5e111bcb63148c9db0c0c09fbc0903812d9435ce9498f37291397d0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "61efa15d8a86a2097b9fa1980497321551c2d068b9bd9ab42bfd6a70427252b3"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a6378a1dd44c292b740a8acf69fd213c1d95485a0b447e38756e31e3c5f8a00c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "03331169e56c64d2ef32c746bb156b3193b7080da87fda2f69defa37cb927b11"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7a2fae3960472d0d97a7adb8e454dfe911317846aa6b2ef2d008d5e5c54ed421"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "3e045731142b6443018c3ca8173928544b7605d24c3142055a8c904755a5d782"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "79aa379c2a68e7cb3ca8e11d6116145302aaa1370907a1f58e036bd3245e38b4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "324119f386de3439cc231eb0c87efbbe4f927ffc599afb87ec9457df6b724470"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/QualityOnDemand/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/QualityOnDemand/documentation/MeetingMinutes/README.md", "original_path": "QualityOnDemand/documentation/MeetingMinutes/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d232321066bf9896e2c15769719e5de79dc22ddb4733289a572e861255545fbc"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RainfallIntensity/README/raw.md", "normalized_path": "original/RainfallIntensity/README.md", "original_path": "RainfallIntensity/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1412ad0ac202edd1c85f7a4ebb6ca00ce1e979620179fdb169962694112ac39a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RainfallIntensity/code/API_definitions/README/raw.md", "normalized_path": "original/RainfallIntensity/code/API_definitions/README.MD", "original_path": "RainfallIntensity/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RainfallIntensity/documentation/API_documentation/README/raw.md", "normalized_path": "original/RainfallIntensity/documentation/API_documentation/README.MD", "original_path": "RainfallIntensity/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RainfallIntensity/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/RainfallIntensity/documentation/SupportingDocuments/README.MD", "original_path": "RainfallIntensity/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/README/raw.md", "normalized_path": "original/RegionDeviceCount/README.md", "original_path": "RegionDeviceCount/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a53d93a5b0f032b7586ff8f8312ccb99114a99727bfdf97532139931f9b8b5f8"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/RegionDeviceCount/code/API_definitions/region-device-count/raw.md", "normalized_path": "original/RegionDeviceCount/code/API_definitions/region-device-count.yaml", "original_path": "RegionDeviceCount/code/API_definitions/region-device-count.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b0b60b590a44bef73759da96ecf34091ecf3a4a92b24a273c2651c00867f6927"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md", "original_path": "RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cc2cd9e76115ca128b74bca65ead4d8690066c41db102dd0a2769d35a76a06bd"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md", "original_path": "RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "66373d1e9d7b8481bf9dabf9329b3ffb246b7cc5ec45c4cd9b0106842b015aa8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist.md", "original_path": "RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "28440dc0246523abe41325a7d063d6ae374f19aba9a7175bf39f043f6c4f92f9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10.md", "original_path": "RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "23caae5a8c68d966853c8543a490f9aa0c2dc39c8f679eebd45ff2d9750a91ba"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/MeetingMinutes/README.MD", "original_path": "RegionDeviceCount/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom/raw.md", "normalized_path": "original/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom.md", "original_path": "RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "39c6b2ba02aaca6bdf3a35b5731f6487609854b654e382f05be3f11dcebfed7c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SessionInsights/README/raw.md", "normalized_path": "original/SessionInsights/README.md", "original_path": "SessionInsights/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a57fdb1ff44ed0eba1a958b1f1c64594aceefc233b80ae1cbc8b0a5a8566ded2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SessionInsights/code/API_definitions/README/raw.md", "normalized_path": "original/SessionInsights/code/API_definitions/README.MD", "original_path": "SessionInsights/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SessionInsights/code/API_definitions/session-insights/raw.md", "normalized_path": "original/SessionInsights/code/API_definitions/session-insights.yaml", "original_path": "SessionInsights/code/API_definitions/session-insights.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c6e3626c884fd78c8d92d1993c81272904ff0bbf98cc24e1a6c960bd655c5465"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SessionInsights/documentation/API_documentation/SessionInsights_User_Story/raw.md", "normalized_path": "original/SessionInsights/documentation/API_documentation/SessionInsights_User_Story.md", "original_path": "SessionInsights/documentation/API_documentation/SessionInsights_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "35f76e0d0c40151996aa43dd56bc77ff08d39f220124a46b9082cb32b3af231a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist/raw.md", "normalized_path": "original/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist.md", "original_path": "SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "78f45e2c290acdff95ac5b3869a1941d473944915fa38cce2bf33144cdf29fc6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/README/raw.md", "normalized_path": "original/ShortMessageService/README.md", "original_path": "ShortMessageService/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "da8623ee9f5c475d4bb65fad6d23ff7dfa17b64afd9a480c18b90d1cc0af8f48"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/code/API_definitions/README/raw.md", "normalized_path": "original/ShortMessageService/code/API_definitions/README.MD", "original_path": "ShortMessageService/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ShortMessageService/code/API_definitions/SMS/raw.md", "normalized_path": "original/ShortMessageService/code/API_definitions/SMS.yaml", "original_path": "ShortMessageService/code/API_definitions/SMS.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bbe66d94ed4bbc7f19089680bbcde6918592fd2ce42021ec978ea8d392d5555e"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription/raw.md", "normalized_path": "original/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription.yaml", "original_path": "ShortMessageService/code/API_definitions/sms-delivery-notification-subscription.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "023d87831f0f08eb6bbbc4de3a4dfa890a7d46bb624f78618fd1591974db62d7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story/raw.md", "normalized_path": "original/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story.md", "original_path": "ShortMessageService/documentation/API_documentation/Text_SMS_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "303931505e4e1fc43323c6eca0f7c2d4bc09b9e1224bde3c6d73ac8dcc8fbc5a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story/raw.md", "normalized_path": "original/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story.MD", "original_path": "ShortMessageService/documentation/API_documentation/binary_SMS_User_Story.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c898a05eacfe3ef3b215f17a081abd1012ed24a97da228fd2672fb9931928e1f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18/raw.md", "normalized_path": "original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18.md", "original_path": "ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "defbabb48f1ab6670b3eaa576cbe6e921bc5ed5520891153c1f464937c15b094"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24/raw.md", "normalized_path": "original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24.md", "original_path": "ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "85845035f836ab4409d8fda809cea9965abca7af7c455b65a2e79e071f37ab10"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31/raw.md", "normalized_path": "original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31.md", "original_path": "ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "492e31f4eb422d27940d01213ba4e437de2e64f1ab6cadf42a86928e2ef33620"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07/raw.md", "normalized_path": "original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07.md", "original_path": "ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cbbd356e6bff3a11f0fd9032a00d9005b2e61d8db765168c911de8dc49bbff08"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/ShortMessageService/documentation/MeetingMinutes/README.MD", "original_path": "ShortMessageService/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "57fe80dfdaf5bf13f89c94836e2cb5991187b2123375aca60159b54e4a4c10a6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/ShortMessageService/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/ShortMessageService/documentation/SupportingDocuments/README.MD", "original_path": "ShortMessageService/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/README/raw.md", "normalized_path": "original/SimSwap/README.md", "original_path": "SimSwap/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a45b518a39533d6d6882fd68ace4b7d4ed30cf939c3131c912c50a87dcd209db"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SimSwap/code/API_definitions/sim-swap-subscriptions/raw.md", "normalized_path": "original/SimSwap/code/API_definitions/sim-swap-subscriptions.yaml", "original_path": "SimSwap/code/API_definitions/sim-swap-subscriptions.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "be5b44d128c0a1d94b382ced4147b3f35ca48424c07a0f6096b9d8f9946fd41d"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SimSwap/code/API_definitions/sim-swap/raw.md", "normalized_path": "original/SimSwap/code/API_definitions/sim-swap.yaml", "original_path": "SimSwap/code/API_definitions/sim-swap.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "51c90816967ee5c22d73a2bcf72b162156f10b1ef064543a78a836d7ff2617ff"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/API_documentation/README/raw.md", "normalized_path": "original/SimSwap/documentation/API_documentation/README.MD", "original_path": "SimSwap/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story/raw.md", "normalized_path": "original/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story.md", "original_path": "SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cb7c3addcb134db80c3cb2b6200ae3d40038c135d5ab8c6232255949aeb7089a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story/raw.md", "normalized_path": "original/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md", "original_path": "SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "48da9a445a6ef78e59aae00b7c2a9cc23288a05eefa15c4a6f7c91d6af7dde48"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist/raw.md", "normalized_path": "original/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist.md", "original_path": "SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "baaeb716b765ccc709ba3da50266920d29bb47e59ca863041f2682ffd12b5457"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist/raw.md", "normalized_path": "original/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist.md", "original_path": "SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8e6e1a0fc7a4a3de6356fdf7247a87e139f546ba51f77f1e33edc3452d9ee3cb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e79a4b6f1a0212147c34ec9e10ef8956cd14f55d757d87224d9853a4acd2a501"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f31c5953c8f219bfb2bf3ee5ab388abbc6e05380c28fe668d915cccc7430f029"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "45bb46795bf6f30bfdf18dfafa9fe3b759bf673fdadcf1ae00387bbeb36b1b5e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "90ec1f57173f4de79c2d8cb9ad9a12d593414d035029c03ac41e0a91ec49ce82"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0a441b0a12a43bd55a25abd7c475b10d467974bfed9f7cd0a30e694917f5e24a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7351a5bfc88dc1ed513b0efcc47ac58c4b3d717b4f9a0d6a5448e37b616786a8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d65c60aeff12b80161facdcde1186782ee5ec4cbbe24515470dc0f79a744f479"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "06e275cc0cdd3c674af3a230d3e890ba3d5227b5ae5b2f7aa5b1efab2dc67f06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "97e1b9f14e7835571c206ba8c75525d7dabea5ebd91cb234c015c8595b753b12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "345d88996323221d9c826e25c9fa5d731adeb8f6fc039fe0228b11da2744eee8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9f7814882220d9785404ea086dff971d92023327a061c6b914e743e9f37a0192"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "baa7c13ce0f25641cd84fa87a9fef7ac7e6c3373869c4bc8b857b0731c7dd538"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "87fe69c7eae3e8cf3b2971c4217d5ef4cca466e414baeab51d56aea63cd4967a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "18bcab5705f1a68b4232cda771e6715dead1ddcb54031cb060ec609681985d7f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b6fb3b7425395cb92cedb8456980339bb6ae3d9d8779c0adfaf30c556befc01a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "91a55df7c866de4cdd0fa1cf7278ca508e6297ff7acb436aff3eab320bb7d810"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d11953ae35553c9f8d4b6e831820d80db787e3a873ff48c3d79d18ed51c2faf1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cbc470b467fae54d2b89e29f3561f82689fc29f6f220e8abd337feae211aa543"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "29a64990b9f722b2b683e36fe3a44b7bbd5ffcd74120bad550f983bfbe27ed06"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d8bcbfbc47707b7c43f4ccf5ba7b98b7054265a8530238bb090b6c588e3cbe12"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ab9b1c82be1f56c7ced701e212d57e006f28995d7214f91fbbb70c97cd56ed7c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "original_path": "SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c17e36ff01a917e24a55ce18e45ac2b831eccac545ffed4afde5afea595aa7b4"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimSwap/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/SimSwap/documentation/MeetingMinutes/README.MD", "original_path": "SimSwap/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a39182018c49815b24bce00835685b14bd8af7d6bb54e48bf353c0d099460ddf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimpleEdgeDiscovery/README/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/README.md", "original_path": "SimpleEdgeDiscovery/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e7ac9bc5a76b544766c9fd3a45a2085464c6634da5965ac45095553b0a8c4a98"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery.yaml", "original_path": "SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "89db6c20443da34d61cefe25885328b3a175e31e23fd809b10cfe75968c80fec"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimpleEdgeDiscovery/documentation/API_documentation/README/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/documentation/API_documentation/README.MD", "original_path": "SimpleEdgeDiscovery/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md", "original_path": "SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c53e7ca82bf21be58298bbbf5e8bbf6ff797117efbee45393100e779bb7e9df2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist.md", "original_path": "SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "24a2d3810051e9d5197c3b3fa388aa3fd9bf19b4e369d682111296da9045cf3e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SimpleEdgeDiscovery/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/SimpleEdgeDiscovery/documentation/SupportingDocuments/README.MD", "original_path": "SimpleEdgeDiscovery/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/README/raw.md", "normalized_path": "original/SiteToCloudVPN/README.md", "original_path": "SiteToCloudVPN/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "641158947aa641fb895faff5c2e94eaac63571c6de27eef4e073515b56914faf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/code/API_definitions/README/raw.md", "normalized_path": "original/SiteToCloudVPN/code/API_definitions/README.MD", "original_path": "SiteToCloudVPN/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8653cae72e25be4354f89a7dd294fa9ae29d65883ad540c800b41f7f8ef08e80"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_/raw.md", "normalized_path": "original/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_.yaml", "original_path": "SiteToCloudVPN/code/API_definitions/S2CVPN3_2_.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1d2bb497c345761421bcf6bfc14705900ed4520717f4609dd63f2b86f18653a9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/API_documentation/README/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/API_documentation/README.MD", "original_path": "SiteToCloudVPN/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story.md", "original_path": "SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c02b305c6c04984d44b7ea5f84d4012ccbaa7c817bed485d068b7f4128a7a374"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12.md", "original_path": "SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5c0468b5a0245ec5ad205b6e8909299c2a7b97c026be68362440ea4b9a6a020b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524.md", "original_path": "SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c10fb46016d0f85f61462e9b2ac3e75c99ab9d397ef764a8f2d2a356a1110e76"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/MeetingMinutes/README.MD", "original_path": "SiteToCloudVPN/documentation/MeetingMinutes/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN.md", "original_path": "SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "768129daff181a46c54f03ba21863429c988237086515c70c11958d2bb59ddb2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/SupportingDocuments/README.MD", "original_path": "SiteToCloudVPN/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements/raw.md", "normalized_path": "original/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements.md", "original_path": "SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "5411597e8ef5b7a53de198e0f04d81e8853308d182689abe8ad04bfce54ff410"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/README/raw.md", "normalized_path": "original/SponsoredData/README.md", "original_path": "SponsoredData/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "78e9ff0089e2c2dee9c0efd6b15ae76af5ca1e61c2f5587ffd7c42e6c302de75"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/code/API_definitions/README/raw.md", "normalized_path": "original/SponsoredData/code/API_definitions/README.MD", "original_path": "SponsoredData/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SponsoredData/code/API_definitions/sponsored_data/raw.md", "normalized_path": "original/SponsoredData/code/API_definitions/sponsored_data.yaml", "original_path": "SponsoredData/code/API_definitions/sponsored_data.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "239f1d5f2c01911aecbbd833fd7ce61b42656d80b785e34d04fa231cd81928bf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/documentation/API_documentation/README/raw.md", "normalized_path": "original/SponsoredData/documentation/API_documentation/README.MD", "original_path": "SponsoredData/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/SponsoredData/documentation/MeetingMinutes/README.md", "original_path": "SponsoredData/documentation/MeetingMinutes/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7eb70257593da06f682a3ddda54a9d260d4fc514f645237f5ca74b08f8da61a6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/documentation/SupportingDocuments/Presentations/README/raw.md", "normalized_path": "original/SponsoredData/documentation/SupportingDocuments/Presentations/README.md", "original_path": "SponsoredData/documentation/SupportingDocuments/Presentations/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7eb70257593da06f682a3ddda54a9d260d4fc514f645237f5ca74b08f8da61a6"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SponsoredData/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/SponsoredData/documentation/SupportingDocuments/README.MD", "original_path": "SponsoredData/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SubscriptionStatus/README/raw.md", "normalized_path": "original/SubscriptionStatus/README.md", "original_path": "SubscriptionStatus/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "407a851d52bc0574b6aed60206be58f2eca3fcab7c2143a520a1dacc53a940e9"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/SubscriptionStatus/code/API_definitions/subscription-status/raw.md", "normalized_path": "original/SubscriptionStatus/code/API_definitions/subscription-status.yaml", "original_path": "SubscriptionStatus/code/API_definitions/subscription-status.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e569d8f38f9166426f087ae881d023e25c93433e05a32c5fdfb1ec9d1ac32ad0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist/raw.md", "normalized_path": "original/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist.md", "original_path": "SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "86a4d7a86971304e550cf8be555fc4fcd31a9ceee328f4f4cabdca1228ba4a55"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/SubscriptionStatus/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/SubscriptionStatus/documentation/SupportingDocuments/README.MD", "original_path": "SubscriptionStatus/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/Tenure/README/raw.md", "normalized_path": "original/Tenure/README.md", "original_path": "Tenure/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "416d3a7ebf4d6e2cedfa6f107f532a98b1aa0f75412a46aea40a70debfc24ceb"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/Tenure/code/API_definitions/kyc-tenure/raw.md", "normalized_path": "original/Tenure/code/API_definitions/kyc-tenure.yaml", "original_path": "Tenure/code/API_definitions/kyc-tenure.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "78ae57d0cb2f4a037b53c3db110a7d6eaa9fcaf1ab27a9f5b119af82aca17ffb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist/raw.md", "normalized_path": "original/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist.md", "original_path": "Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "12920be64be6db46fce834e1f2a6507699b9f18e5a738a746af6673ba6968204"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/Tenure/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/Tenure/documentation/SupportingDocuments/README.MD", "original_path": "Tenure/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/TrafficInfluence/README/raw.md", "normalized_path": "original/TrafficInfluence/README.md", "original_path": "TrafficInfluence/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c129d1c5a8214b0f9e43326c7fd3e56ae86ce77618ab631f5d78ab706a4ce725"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/TrafficInfluence/code/API_definitions/traffic-influence/raw.md", "normalized_path": "original/TrafficInfluence/code/API_definitions/traffic-influence.yaml", "original_path": "TrafficInfluence/code/API_definitions/traffic-influence.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "78a6a6163391d9f99050951d0e99fbf89cd284ea49c3fb29f6f59fcde3a13c67"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist/raw.md", "normalized_path": "original/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist.md", "original_path": "TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "329af1128cdc0c2917f60749dba7c7355ad398753be18f888139338349da1773"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1/raw.md", "normalized_path": "original/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1.md", "original_path": "TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bb64ebe62577d166fad3ef273ef5685012cd36afff51c9a9bf2ed0f48b8495e8"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/TrafficInfluence/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/TrafficInfluence/documentation/SupportingDocuments/README.MD", "original_path": "TrafficInfluence/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VerifiedCaller/README/raw.md", "normalized_path": "original/VerifiedCaller/README.md", "original_path": "VerifiedCaller/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6275b882650550d59debefd08d3ad24edd9596c7fcb0b8f64e2b5cd43704f48f"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/VerifiedCaller/code/API_definitions/brand-registration/raw.md", "normalized_path": "original/VerifiedCaller/code/API_definitions/brand-registration.yaml", "original_path": "VerifiedCaller/code/API_definitions/brand-registration.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "df6e7a607e44dd1baa5e02ff493ac07538c6fb133af47723760bd522c3905289"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/VerifiedCaller/code/API_definitions/verified-caller/raw.md", "normalized_path": "original/VerifiedCaller/code/API_definitions/verified-caller.yaml", "original_path": "VerifiedCaller/code/API_definitions/verified-caller.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "a12cd4dbcbccd66dd9c542126add30ff5561961e08a3056d3e863571494835b0"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story/raw.md", "normalized_path": "original/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story.md", "original_path": "VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7d434a271f5d443dd16416f8d1c27ca17485291e1de69097db336fa99ecfef69"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist/raw.md", "normalized_path": "original/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist.md", "original_path": "VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "da2586f43d310375a8cc877113f13c897bf83f7bf1579eebe174360f639a1641"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist/raw.md", "normalized_path": "original/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist.md", "original_path": "VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "4704712f106921f29d4362d007fa05b1e06caec51d7b99de11ef6fba0e20e4a9"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceNotification/README/raw.md", "normalized_path": "original/VoiceNotification/README.md", "original_path": "VoiceNotification/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "e6aff4ced8c4444f2e9f44f972fe0e9ed7635b5109f4672bbe95d62ee0429896"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceNotification/code/API_definitions/README/raw.md", "normalized_path": "original/VoiceNotification/code/API_definitions/README.MD", "original_path": "VoiceNotification/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceNotification/documentation/API_documentation/README/raw.md", "normalized_path": "original/VoiceNotification/documentation/API_documentation/README.MD", "original_path": "VoiceNotification/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceNotification/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/VoiceNotification/documentation/SupportingDocuments/README.MD", "original_path": "VoiceNotification/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceVerificationCode/README/raw.md", "normalized_path": "original/VoiceVerificationCode/README.md", "original_path": "VoiceVerificationCode/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8a36aeead5e57df566b34f6f63f3dd0be2d651b441e9cc678795a12a95cefc28"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceVerificationCode/code/API_definitions/README/raw.md", "normalized_path": "original/VoiceVerificationCode/code/API_definitions/README.MD", "original_path": "VoiceVerificationCode/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceVerificationCode/documentation/API_documentation/README/raw.md", "normalized_path": "original/VoiceVerificationCode/documentation/API_documentation/README.MD", "original_path": "VoiceVerificationCode/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/VoiceVerificationCode/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/VoiceVerificationCode/documentation/SupportingDocuments/README.MD", "original_path": "VoiceVerificationCode/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/README/raw.md", "normalized_path": "original/WebRTC/README.md", "original_path": "WebRTC/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "b02f934ad4107b2bbf72f65c58a152d62f11323ee631630921b18d7c0b2327ab"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/code/API_definitions/README/raw.md", "normalized_path": "original/WebRTC/code/API_definitions/README.MD", "original_path": "WebRTC/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "9537a4cb0eb4a134430da4557609bce6ed1f24c551bf594f8c8dbfdd4309c796"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/WebRTC/code/API_definitions/webrtc-call-handling/raw.md", "normalized_path": "original/WebRTC/code/API_definitions/webrtc-call-handling.yaml", "original_path": "WebRTC/code/API_definitions/webrtc-call-handling.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "820c4d50958f233858acbdad9ee4e1edeab2e09c41c312869f6bef81e852615c"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/WebRTC/code/API_definitions/webrtc-events/raw.md", "normalized_path": "original/WebRTC/code/API_definitions/webrtc-events.yaml", "original_path": "WebRTC/code/API_definitions/webrtc-events.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c828d58fe2c7b57335c8b7524ec3d8b34c66c63a769960614bf475941999b2ed"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/WebRTC/code/API_definitions/webrtc-registration/raw.md", "normalized_path": "original/WebRTC/code/API_definitions/webrtc-registration.yaml", "original_path": "WebRTC/code/API_definitions/webrtc-registration.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cc326f845f5ad2a56a1126b7c6070d0cc8dfaa559b2b4419bd537886692b8bcf"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist/raw.md", "normalized_path": "original/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist.md", "original_path": "WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "70fc825624ddc0af9de73e23fb1e2de10eafe372e80586e92a7a74e4695f9510"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist/raw.md", "normalized_path": "original/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist.md", "original_path": "WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cda656c9cc3e92617f903e45221f8e5b308647c464fda8cfbd0c1e91aa4beb47"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist/raw.md", "normalized_path": "original/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist.md", "original_path": "WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "7959d63be6df9277e9eaca32121ca2afc79238cd7131cce3a91e0df3fbc80cac"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_231023/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_231023.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_231023.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "d00b865e2a8a8a0175692127163b1e62f03677a3573271da59214a09df9d9223"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_231106/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_231106.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_231106.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6a2fe56dfa171a8a9e4413120212ea3c443f3c736aabc32749cc34196d24d71f"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_231120/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_231120.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_231120.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "11d37b75e031c4762df32f8baa72f7b42074a598ac2d26d7470903986fe53b52"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_231205/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_231205.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_231205.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "63f6c2fc17389b0349f145f4d974b9f9a24442df86508388cec796ea306ae1a1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_231219/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_231219.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_231219.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8afc4690cb0cb347c988de5fb7fdc9a7430e90ee0eabafe1a36ec6da5c9e447b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_240116/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_240116.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_240116.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "76333a5f93107b5e11ab21881dcb30f4ee4c372d2e6a7dbe2ccfa9736d3005c5"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_240130/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_240130.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_240130.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ea387509ee9cc2ce3e98090f2b6b4e4330066996988522f40d31e826b9748d8d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_240213/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_240213.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_240213.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "8112b383b6d640fdeb9096d2f6d39373013d98a57036635217f254f75e4e0daa"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_240227/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_240227.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_240227.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55f62c1ad1fbb95fd15242bac0377156c0449beaafdf4acab021cd6ba91e4114"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/MoM_240312/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/MoM_240312.md", "original_path": "WebRTC/documentation/MeetingMinutes/MoM_240312.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "10cf507f6e90c8e1dfb3cd6c4853348440ab85d4c49a168b8c3d637104403ef2"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/MeetingMinutes/README/raw.md", "normalized_path": "original/WebRTC/documentation/MeetingMinutes/README.md", "original_path": "WebRTC/documentation/MeetingMinutes/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2ea1ca24a9b64510b27d70ee9933f62acbc7a97df03cf1263f3ca345369a852d"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/README/raw.md", "normalized_path": "original/WebRTC/documentation/README.md", "original_path": "WebRTC/documentation/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "bed2c18ca35f3f60c8f1a53740179c93baa2ce983678735d267c90556717c49e"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/README.md", "original_path": "WebRTC/documentation/SupportingDocuments/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "55e6275dd6674d038e2ff02aa33926ebc7fcf30f536e7d4c8b430e5def138728"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW.md", "original_path": "WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "eff933c56ff6272f1b45ef09a279039de8947c8398f0d2b29d9a937385d4c21a"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/uml-diagrams/README/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/uml-diagrams/README.md", "original_path": "WebRTC/documentation/SupportingDocuments/uml-diagrams/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "ccedce83013d554732a76bace747fd932ec4502c0cc092b61371645b4a0b2325"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README.md", "original_path": "WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6c3036aa67c3ed497220b10f6ef7aef64a6ed264bb073d0d638dee272ef3edc1"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection.md", "original_path": "WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "2f7be80d1c6bd875f0d3854a9e0216725367e59208b660ca360bd05bd009cf54"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events.md", "original_path": "WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "cf711b97ae77b0538467a953e2211363cf043202a879cfd941dadc066586e244"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration.md", "original_path": "WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "1188eae6f4acdceaed4e634f72c4e77c575567a15a03a210250b10f73606e926"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering.md", "original_path": "WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "f9fce68fa3fe6b11a7b0c03b3990ba8bc0c9080d9f18a844440bb649582f49eb"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/WebRTC/documentation/SupportingDocuments/webrtc_voice_api/raw.md", "normalized_path": "original/WebRTC/documentation/SupportingDocuments/webrtc_voice_api.md", "original_path": "WebRTC/documentation/SupportingDocuments/webrtc_voice_api.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "eb0b592a34bec601dbb25d55c41539c9105517e64dd3ca008b6c4dc99fe71b91"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/eSimRemoteManagement/README/raw.md", "normalized_path": "original/eSimRemoteManagement/README.md", "original_path": "eSimRemoteManagement/README.md", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "c168b43c0bb213ab98b34e6b59729528fbe9dede5dea3e508cef77f8cb74a073"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/eSimRemoteManagement/code/API_definitions/README/raw.md", "normalized_path": "original/eSimRemoteManagement/code/API_definitions/README.MD", "original_path": "eSimRemoteManagement/code/API_definitions/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "6d31bf5394eb7f88b72033b0e3620e42805dcfefdcebbbebd8e063f4b3bc9ca7"} +{"body": "camara", "file_type": ".yaml", "marked_path": "marked/eSimRemoteManagement/code/API_definitions/esim-remote-management/raw.md", "normalized_path": "original/eSimRemoteManagement/code/API_definitions/esim-remote-management.yaml", "original_path": "eSimRemoteManagement/code/API_definitions/esim-remote-management.yaml", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0e1801b75f5b7a6bf8518ad685ebd03f06a664eacbc8652375f32e1195a2a26b"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/eSimRemoteManagement/documentation/API_documentation/README/raw.md", "normalized_path": "original/eSimRemoteManagement/documentation/API_documentation/README.MD", "original_path": "eSimRemoteManagement/documentation/API_documentation/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} +{"body": "camara", "file_type": ".md", "marked_path": "marked/eSimRemoteManagement/documentation/SupportingDocuments/README/raw.md", "normalized_path": "original/eSimRemoteManagement/documentation/SupportingDocuments/README.MD", "original_path": "eSimRemoteManagement/documentation/SupportingDocuments/README.MD", "parse_status": "OK", "reason": "parsed", "section": "original", "sha256": "0ed5e4de94c87477a493b6c5a8d9f6b9d2a2ca6bcf1a1ca3d9b32e53bae3fd0c"} diff --git a/marked/ApplicationEndpointDiscovery/README/raw.md b/marked/ApplicationEndpointDiscovery/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9936371efe0978c0187e0d5f53a902b3c1e927f1 --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationEndpointDiscovery + +Sandbox API Repository to describe, develop, document, and test the ApplicationEndpointDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAtC) + +## Scope + +* Service API(s) “ApplicationEndpointDiscovery” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Discover the optimal application endpoint(s) that a given end-user's device can connect to. +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationEndpointDiscovery/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-endpoint-discovery v0.1.0** + [[YAML]](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/r1.2/code/API_definitions/application-endpoint-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointDiscovery/r1.2/code/API_definitions/application-endpoint-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointDiscovery/r1.2/code/API_definitions/application-endpoint-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationEndpointDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationEndpointDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery/raw.md b/marked/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a79ca64674dcc49c046eadc03a3b04ed81767315 --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery/raw.md @@ -0,0 +1,912 @@ +# application-endpoint-discovery + +```yaml +--- +openapi: 3.0.3 +info: + title: Application Endpoint Discovery + version: wip + description: | + The Application Endpoint Discovery API returns the optimal application + endpoint(s) that a given end-user's device can connect to. + + # Introduction + + Operators often host multiple Edge Cloud Zones across various territories. + Connecting an application directly to the optimal application instance + endpoint in an Edge Cloud Zone may minimize latency. + + The Application Endpoint Discovery API extends beyond the capabilities of + the Simple Edge Discovery API by not only locating the optimal + Edge Cloud Zone but also providing the direct link to the specified + application's endpoint within that Edge Cloud Zone. This approach ensures + that developers can instantly integrate this endpoint into their + applications, improving user experience. + + After identifying the optimal application endpoint(s) through the API, + API consumers can: + * Connect their application client directly to the chosen application + endpoint(s), enhancing the responsiveness of the service. + * If no suitable endpoints are available, the developer can use other APIs + to instantiate new instance and/or register new application endpoints. + + The optimal endpoint(s) are calculated by the Edge Cloud Provider based on + the following factor: shortest network path to the network-attached + device identified in the API request. Future releases of this API might + add other factors to obtain them. + + # Relevant terms and definitions + + - `Application Profile:` A profile which represents an application's + networking demands (latency, jitter, bandwidth rates). + - `Application Provider:` The provider of the application that is deployed + on the Edge Cloud. + - `Application Endpoint:` An application server IP address or FQDN, and + port exposed by an application instance to allow connections from clients. + - `Application Instance:` An instantiation of an Application running on + an Edge Cloud Zone. It is assumed that for each application, a maximum of + one logical instance can run per Edge Cloud Zone. + - `Device:` End-user equipment able to connect to a mobile network (i.e. + smartphone, IoT sensor/actuator). + - `Edge Cloud Zone:` Availability Zone in an Edge Cloud. It is the lowest + level of abstraction exposed to an Application Provider who wants to + deploy an Application on Edge Cloud. Availability Zones exist within + a Region. + + # API Functionality + + The API can be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet), or by a server. + + There is a single API service endpoint: + + - `POST /retrieve-optimal-app-endpoints` + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `device:` End-user equipment able to connect to a mobile network. The + developer can choose to provide the below specified device identifiers: + - `ipv4Address:` Public IP address (IPv4) of the user device, which can be + fetched via external IP discovery services. + - `ipv6Address:` Public IP address (IPv6) of the user device, which can be + fetched via external IP discovery services. + - `phoneNumber:` The device's phone number in international E.164 format. + - `networkAccessIdentifier:` A unique identifier provided by the network + operator (where supported). + - One of the following application identifiers: + - `appId:` A unique identifier for an application onboarded on the Edge + Cloud. It is used when the application has been onboarded using the Edge + Application Management API. + - `applicationEndpointsId:` A unique identifier for the registered + application endpoint(s). It is used when the application has not been onboarded + using the Edge Application Management API, and available endpoints have been + registered by the Edge Application Registration API. Every endpoint registered + under the same `applicationEndpointsId` identifier belongs to the same + application. + + ## Outputs + + If successful, a `200 OK ` response code is returned with a JSON object + containing the following data: + + - `applicationEndpoints:` An array containing at least one Application Endpoint + object. Each Application Endpoint object includes the following parameters: + - `port:` TCP or UDP port number exposed by the application instance. + - One of the following parameters which define the endpoint: + - `ipv4addresses:` Array of IPv4 addresses exposed by the application + instance. + - `ipv6addresses:` Array of IPv6 addresses exposed by the application + instance. + - `fqdn:` Fully Qualified Domain Name exposed by the application instance. + - `applicationEndpointDescription:` Optionally, a string that describes the + application endpoint. + - `edgeCloudZone:` Optionally, object that identifies the Edge Cloud Zone + the application endpoint belongs to, including: `edgeCloudZoneId`, + `edgeCloudZoneName`, `edgeCloudZoneStatus`, `edgeCloudRegion`, and + `edgeCloudProvider`. + - One of the following application identifiers (the one provided on the request) + - `appId:` A unique identifier for an application onboarded on the Edge + Cloud. It is used when the application has been onboarded using the Edge + Application Management API. + - `applicationEndpointsId:` A unique identifier for the registered + application endpoint(s). It is used when the application has not been onboarded + using the Edge Application Management API, and available endpoints have been + registered by the Edge Application Registration API. Every endpoint + registered under the same `applicationEndpointsId` identifier belongs to + the same application. + - `applicationServerProviderName:` Optionally, the Application Provider + identifier + - `applicationProfileId:` Optionally, the Application Profile identifier + - `device`: End-user equipment identifier used to obtain the optimal application + endpoint. It is only included when multiple device identifiers come in the + request. + - The `Device` object allows the API consumer to provide more than one device + identifier. No error will be returned when the supplied device identifiers + do not match with the same device. It is responsibility of the API consumer + to ensure that the identifiers they are using are associated with the same + device. + - Where an API consumer provides more than one device identifier, the + response will indicate which of these identifiers have been used to fulfil + the API, even if the identifiers do not match the same device. The + `DeviceResponse` object is defined for this purpose. + + + ## Errors + + - If the API call contains a formatting or other any other syntatic error, + a `400 INVALID_ARGUMENT` error is returned. + - If the API call cannot be authenticated due to missing, invalid, or + expired credentials, a `401 UNAUTHENTICATED` error is returned. + - If the API call has a valid access token that does not have the + required scope, then a `403 PERMISSION_DENIED` error is returned. + - If the API call has a valid access token that does not identify + a single device, then a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API call has an `appId` that does not identify a valid + application on the Edge Cloud, a `404 NOT_FOUND` error is returned. + - If the API call has an `applicationEndpointsId` that does not identify + any registered endpoint on the Edge Cloud, a `404 NOT_FOUND` error + is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will + be identified from the optional `device` object, which therefore MUST be + provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged + access token to invoke the API by relying on the information that is + associated with the access token and was identified during the + authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `device` object is not included in the request, then the server + will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional + `device` object is also included in the request, then the server will + return an error with the `422 UNNECESSARY_IDENTIFIER` error code. + This will be the case even if the same device is identified by + these two methods, as the server is unable to make this comparison. + - If the subject cannot be identified from the access token and the + optional `device` object only includes device identifiers not supported + by the implementation, then the server will return an error with the + `422 UNSUPPORTED_IDENTIFIER` error code. + - If the service is not applicable for the subject that is identified + from the access token or the optional `device` object, then the server + will return an error code with the `422 SERVICE_NOT_APPLICABLE` error + code. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + --- + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ApplicationEndpointDiscovery +servers: + - url: "{apiRoot}/application-endpoint-discovery/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by the service provider, e.g. `api.example.com` or + `api.example.com/somepath` + +tags: + - name: Application Endpoint Discovery + description: | + Find the optimal Application Instance Endpoint(s) to the user device. +paths: + /retrieve-optimal-app-endpoints: + post: + security: + - openId: + - application-endpoint-discovery:app-endpoints:read + operationId: getOptimalAppEndpoints + parameters: + - name: x-correlator + in: header + required: false + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/EndpointDiscoveryInfo" + examples: + Identify Device By 3-Legged Access Token and AppId: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedTokenAppId' + Identify Device By Phone Number and AppId: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumberAppId' + Identify Device By IP Address and ApplicationEndpointsId: + $ref: '#/components/examples/IdentifyDeviceByIPAddressAppEndpointsId' + Identify Device By Multiple Identifiers and AppId: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiersAppId' + responses: + "200": + description: | + Successful response, returning the optimal Application Instance + Endpoint(s) to the user device identified in the request body. + The response will include the endpoint(s) exposed by the Application + Instance(s) with the shortest network path to the end user device + identified in the request. There can be multiple application endpoints + returned in the response and the API consumer can choose the one that best + suits their needs. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/EndpointDiscoveryResult" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Application Endpoint Discovery + summary: | + Returns the Endpoint(s) of the optimal Application Instance(s) to the user + device identified in the request. + description: | + On receiving this request, the network will return the endpoint(s) + of the Application Instance(s) with the shortest network path to the + end user device identified in the request. +components: + securitySchemes: + openId: + description: OpenID Provider Configuration Information. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified + device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these + options. The API invoker can provide multiple identifiers to be + compatible across different network operators. In this case the + identifiers MUST belong to the same device. + + NOTE2: as for this Commonalities release, we are enforcing that + the networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/SingleIpv6Addr" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the + network that the response refers to. This parameter is only + returned when the API consumer includes the `device` parameter in + their request (i.e. they are using a two-legged access token), and + is relevant when more than one device identifier is specified, as + only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in + their request, the API provider must return a single identifier + which is the one they are using to fulfil the request, even if the + identifiers do not match the same device. API provider does not + perform any logic to validate/correlate that the indicated device + identifiers match the same device. No error should be returned if + the identifiers are otherwise valid to prevent API consumers + correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has + to be formatted in international format, according to E.164 + standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. + In 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least + one of either privateAddress or publicPort, dependent upon which is + known. In general, mobile devices cannot be identified by their + public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + SingleIpv6Addr: + description: | + The device should be identified by the observed IPv6 address, or by + any single IPv6 address from within the subnet allocated to the + device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + EndpointDiscoveryInfo: + description: | + Element to retrieve the optimal application endpoint(s) for the + identified device. + type: object + anyOf: + - required: [applicationEndpointsId] + - required: [appId] + properties: + device: + $ref: "#/components/schemas/Device" + applicationEndpointsId: + $ref: "#/components/schemas/ApplicationEndpointsId" + appId: + $ref: "#/components/schemas/AppId" + + ApplicationEndpointsId: + description: | + A system-defined string identifier representing + one or more registered Application Endpoints that belong + to the same application. + type: string + format: uuid + example: "4d596ac1-7822-4927-a3c5-d72e1f922c94" + + AppId: + type: string + format: uuid + description: | + A globally unique identifier associated with the application. + This GUID will have been previously provided by the Edge Cloud Zone + provider. + example: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + EndpointDiscoveryResult: + description: | + Endpoint Discovery result including optimal application endpoint(s) + for the requested identified device. + type: object + required: + - applicationEndpoints + anyOf: + - required: [applicationEndpointsId] + - required: [appId] + properties: + applicationEndpoints: + description: Array of Application Endpoints. + type: array + items: + $ref: "#/components/schemas/ApplicationEndpoint" + minItems: 1 + appId: + $ref: "#/components/schemas/AppId" + applicationEndpointsId: + $ref: "#/components/schemas/ApplicationEndpointsId" + applicationServerProviderName: + type: string + description: Unique ID representing the Edge Application Provider + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/DeviceResponse" + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + + EdgeCloudZoneId: + description: A unique identifier for the Edge Cloud Zone. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + EdgeCloudRegion: + description: | + The EdgeCloudProvider's name for the region where the Edge Cloud + Zone is located. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + EdgeCloudProvider: + description: The provider of the Edge Cloud. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ProviderA" + + EdgeCloudZoneName: + description: The name of the Edge Cloud Zone. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ZoneA" + + ApplicationProfileId: + description: A unique identifier for the application profile. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + ApplicationEndpoint: + type: object + description: | + An application server IP address or FQDN with a port, + exposed by an application instance deployed on the Edge Cloud + provider. + required: + - port + anyOf: + - required: [fqdn] + - required: [ipv4Addresses] + - required: [ipv6Addresses] + properties: + fqdn: + $ref: "#/components/schemas/Fqdn" + ipv4Addresses: + description: Array of IPv4 addresses. + type: array + items: + $ref: "#/components/schemas/Ipv4Address" + minItems: 1 + ipv6Addresses: + description: Array of IPv6 addresses. + type: array + items: + $ref: "#/components/schemas/Ipv6Address" + minItems: 1 + port: + $ref: "#/components/schemas/Port" + edgeCloudZone: + $ref: "#/components/schemas/EdgeCloudZone" + applicationEndpointDescription: + type: string + description: Description of the application endpoint + + Fqdn: + type: string + description: Fully Qualified Domain Name. + + Ipv4Address: + type: string + description: | + A single IPv4 address specified in dotted-quad form like 1.2.3.4. + example: "198.51.100.1" + + Ipv6Address: + type: string + description: | + A single IPv6 address, following IETF 5952 format like + 2001:db8:85a3:8d3:1319:8a2e:370:7344. + example: "2001:db8:85a3::8a2e:370:7334" + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: | + Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter criteria + combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: | + Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: | + Permission denied. OAuth2 token access does not have the + required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: | + Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: | + An identifier is not included in the request and the device or phone + number identification cannot be derived from the 3-legged access + token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: | + None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: | + An explicit identifier is provided when a device or phone + number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: | + Access to the API has been temporarily blocked due to rate or spike + arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedTokenAppId: + description: Empty JSON when device is identified by access token + value: + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + IdentifyDeviceByPhoneNumberAppId: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + IdentifyDeviceByIPAddressAppEndpointsId: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + applicationEndpointsId: "4d596ac1-7822-4927-a3c5-d72e1f922c94" + + IdentifyDeviceByMultipleIdentifiersAppId: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" +``` diff --git a/marked/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist/raw.md b/marked/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..567f7ae0f70408ccadae804ceb5054dd324660cb --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# Application Endpoint Discovery API Readiness minimum criteria checklist + +Checklist for Application-Endpoint-Discovery v0.1.0 + +| Nr | API release assets | alpha | release-candidate | initial
public | stable
public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-endpoint-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y |[r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/SupportingDocuments/API_Documentation/User%20Stories/Application%20Endpoint%20Discovery%20User%20Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-endpoint-discovery.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.MD) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/137166903/ApplicationEndpointDiscovery+API+description) | diff --git a/marked/ApplicationEndpointDiscovery/documentation/API_documentation/README/raw.md b/marked/ApplicationEndpointDiscovery/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story/raw.md b/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a273473214dabf6eef815300fc1f40723f302d19 --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story/raw.md @@ -0,0 +1,84 @@ +# Application Endpoint Discovery API User Story + +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)_ + +| **Item** | **Details** | +| ---- | ------- | +| **_Summary_** | As an application developer belonging to an enterprise, I want to discover (using either my application server/backend service, or an HTTP application client on the end-user device) the optimal application instance running in an Edge Cloud Zone that a given end-user's device can connect to. | +| **_Roles and Actors and Scope_** | **Roles:** Customer:User
**Actors:** Application service providers, network operators, application developers. The API allows a check to see if end-user consent is required: if consent is required, the end-user will be an actor in the consent flow.
**Scope:** Get the endpoint of the application hosted at the optimal Edge Cloud Zone | +| **_Pre-conditions_** |The preconditions are listed below:
  1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
  2. The Customer:BusinessManager has successfully subscribed to the Application Endpoint Discovery product from the product catalog.
  3. The Customer:Administrator has onboarded the Customer:User to the platform.
  4. The Customer:User has obtained a valid identifier for the target device, or, will make the API request from an application client on a device connected to the operator's network.
  5. | +| **_Begins when_** | The customer application server/client makes a POST request to the Application Endpoint Discovery API to query the optimal Application Endpoint to the target device (an end-user device). The target device is either identified either in a 3-legged consent flow including a device object, or by device identifier(s) in the request body.| +| **_Ends when_** | The Application Endpoint Discovery API returns the endpoint(s) of the optimal application instance(s) for this user.| +| **_Post-conditions_** | Optional - the customer may decide to act upon the information by connecting the end-user application client to the application server instance hosted at one of the received Application Endpoints. | +| **_Exceptions_** | Several exceptions might occur during the API operations:
    - Unauthorized: Invalid credentials (e.g., expired access token).
    - Incorrect input data (e.g., malformed phone number).
    - Not found: The phone number is not associated with a CSP customer account, the application does not have any running instances in the Edge Cloud, or the application endpoint ID received in the request is not registered in the Edge Cloud. | + +## API Workflows + +### Scenario 1: direct request from application client or end-user device + +Constraints: + +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: browser or app calls API over HTTPS +- Northbound Interface only (no 'UNI' client SDK required) +- The call must include an application identifier (_appId_) which must be provided by the Application Provider. + +Note: + +- the Edge Cloud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + autonumber + participant Application Client + participant Operator + participant Edge Cloud Zone + Note over Application Client, Operator: PRE developer has acquired an identifier for the device in question + Note over Application Client, Operator: PRE App developer registered, authenticated and authorised + Note over Application Client, Operator: PRE Application instances are up and running on one or several Edge Cloud Zones + + Application Client->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), appId}` + Operator->>Operator: Calculate optimal Application Endpoint(s) + Operator->>Application Client: optimal Application Endpoint(s) + opt connect to optimal instance endpoint + Application Client->>Edge Cloud Zone: Connect to optimal instance endpoint + end +``` + +### Scenario 2: request from developer server + +Constraints: + +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: none, browser or app calls API over HTTPs (no client SDK required) +- Dependencies: + - the call must include an identifier for the device (device) for which 'optimal MEC' is being calculated + - the call must include an application identifier: + - _appId_ (application identifier) in case the application is deployed by Edge Application Management API + - _applicationEndpointsId_ (registered endpoints identifier) for other cases. It requires previous registration of application endpoints using Application Endpoint Registration API. + +Note: the Edge CLoud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + autonumber + participant Application Client + participant Application Server + participant Operator + participant Edge Cloud Zone + Note over Application Server, Operator: PRE developer has acquired an identifier for the device in question + Note over Application Server, Operator: PRE App developer registered, authenticated and authorised + Note over Application Server, Operator: PRE Application instances are up and running on one or several Edge Cloud Zones + alt The application has been deployed with Edge Application Management API + Application Server->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), appId}` + else The application has not been instantiated with Edge Application Management API + Note over Application Server,Operator: PRE Application Endpoints have been registered in Operator Platform + Application Server->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), applicationEndpointsId}` + end + Operator->>Operator: Calculate optimal Application Endpoint(s) + Operator->>Application Server: optimal Application Endpoint(s) + opt inform app so it connects to the instance endpoint + Application Server->>Application Client: report optimal Application Endpoint + Application Client->>Edge Cloud Zone: Connect to instance endpoint + end +``` diff --git a/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README/raw.md b/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ApplicationEndpointRegistration/README/raw.md b/marked/ApplicationEndpointRegistration/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5ab4f63d39396dbb954447bc6d9708e1d2c473b1 --- /dev/null +++ b/marked/ApplicationEndpointRegistration/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationEndpointRegistration + +Sandbox API Repository to describe, develop, document, and test the ApplicationEndpointRegistration Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAsC) + +## Scope + +* Service API(s) “ApplicationEndpointRegistration” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * register the endpoints of an application which is deployed across various Edge Cloud Zones +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationEndpointRegistration/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-endpoint-registration v0.1.0** + [[YAML]](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/r1.2/code/API_definitions/application-endpoint-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointRegistration/r1.2/code/API_definitions/application-endpoint-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointRegistration/r1.2/code/API_definitions/application-endpoint-registration.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationEndpointRegistration/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationEndpointRegistration/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ApplicationEndpointRegistration/code/API_definitions/README/raw.md b/marked/ApplicationEndpointRegistration/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/ApplicationEndpointRegistration/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration/raw.md b/marked/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..55197024a611b3c59f54d98d5e8214b3467bc106 --- /dev/null +++ b/marked/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration/raw.md @@ -0,0 +1,763 @@ +# application-endpoint-registration + +```yaml +--- +openapi: 3.0.3 +info: + title: Application Endpoints Registration + version: wip + x-camara-commonalities: 0.6 + description: | + The Application Endpoints Registration API provides a programmable + interface for developers to register the endpoints of an application + which is deployed across various Edge Cloud Zones. + It allows developers to retrieve, update, and delete those registrations. + + # Introduction + + The API registers the Application Endpoints. + This information can be used for various use cases like optimal endpoint + discovery to help end users connect to the most optimal instance of the + application which is distributed across various Edge Cloud Zones. + Additionally the information can be used to monitor the edge instances to + take decisions from a lifecycle management perspective. The API provides + the ability to register, read and manage the deployed edge instances of + the application. + + # Relevant terms and definitions + + * **Application Endpoint**: + + The Endpoint on which the application is accessible. + It can be a FQDN, IPv4, or IPv6 address with a port number. + + * **Application Profile**: + + It represents the application's network and + compute characteristics. This helps distinguish between different + applications and their specific requirements. + + * **Edge Cloud Zone**: + + Availability Zone in an Edge Cloud. It is the lowest + level of abstraction exposed to an Application Provider who wants to + deploy an Application on Edge Cloud. Availability Zones exist within + a Region. + + # API functionality + + The API provides the following operations: + - POST registerApplicationEndpoints: Registers the Application Endpoints + of a deployed application to a specified edge cloud zone. + - GET getAllRegisteredApplicationEndpoints: Returns endpoint information for + all registered Applications. + - GET getApplicationEndpointsByID: Returns endpoint information for all + Applications registered to a specified applicationEndpointListId. + - PUT updateApplicationEndpoint: Update registered application endpoint + information. + - DELETE deregisterApplicationEndpoint: Deregister an application's + Endpoints. + ## Errors + + - If the API call contains a formatting or any other syntactic error, + a `400 INVALID_ARGUMENT` error is returned. + - If the API call cannot be authenticated due to missing, invalid, or + expired credentials, a `401 UNAUTHENTICATED` error is returned. + - If the API call has a valid access token that does not have the + required scope, then a `403 PERMISSION_DENIED` error is returned. + - If the API call has an `applicationEndpointListId` that does not identify + any registered endpoint on the Edge Cloud, a `404 NOT_FOUND` error + is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Further info and support + + [GSMA Mobile Connect Account Takeover Protection specification] + (https://www.gsma.com/identity/wp-content/uploads/2022/12/IDY.24-Mobile- + Connect-Account-Takeover-Protection-Definition-and-Technical-Requirements- + v2.0.pdf) + was used as source of input for this API. For more about Mobile Connect, + please see [Mobile Connect website](https://mobileconnect.io/). + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/ApplicationEndpointRegistration + +servers: + - url: "{apiRoot}/application-endpoint-registration/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application Endpoint Registration + description: | + Operations to register, read and manage deployed instances of the + application. + +paths: + /application-endpoint-lists: + post: + security: + - openId: + - application-endpoint-registration:application-endpoints:write + tags: + - Application Endpoint Registration + summary: Register endpoints of a deployed application + description: | + Register the endpoints of a deployed application + to a specified edge cloud zone. + operationId: registerApplicationEndpoints + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Array of Application Endpoints for an + application deployed across various Edge Cloud Zones. + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + responses: + "200": + description: Returns an applicationEndpointListId + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointListId" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - application-endpoint-registration:application-endpoints:read + tags: + - Application Endpoint Registration + summary: Get all registered edge application endpoint information + description: | + Returns endpoint information for all + registered Applications. + operationId: getAllRegisteredApplicationEndpoints + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Array of registered Application Endpoints + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/ApplicationEndpointList" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + "/application-endpoint-lists/{applicationEndpointListId}": + parameters: + - name: applicationEndpointListId + in: path + description: The unique identifier for the application endpoints + that got created when registering the application endpoints. + required: true + schema: + $ref: "#/components/schemas/ApplicationEndpointListId" + - $ref: "#/components/parameters/x-correlator" + get: + security: + - openId: + - application-endpoint-registration:application-endpoints:read + tags: + - Application Endpoint Registration + summary: Get registered edge application endpoint information + description: | + Returns endpoint information of the application based on + applicationEndpointListId. + operationId: getApplicationEndpointsById + responses: + "200": + description: Application Endpoint information based on + given ApplicationEndpointListID + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointList" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + put: + security: + - openId: + - application-endpoint-registration:application-endpoints:update + tags: + - Application Endpoint Registration + summary: Update an application Endpoint + description: | + Update registered application Endpoint information. + operationId: updateApplicationEndpoint + requestBody: + description: Application Endpoint information + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + responses: + "204": + description: Updates Application Endpoint Information + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + delete: + security: + - openId: + - application-endpoint-registration:application-endpoints:delete + tags: + - Application Endpoint Registration + summary: Deregister an application Endpoint + description: | + Deregister an application's + Endpoint from the edge cloud zone. + operationId: deregisterApplicationEndpoint + responses: + "204": + description: Deregister Application Endpoint + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + ApplicationEndpointsInfo: + description: Endpoint information of the Application + deployed across different Edge Cloud Zones. + type: object + properties: + applicationEndpoints: + type: array + description: List of endpoints of the application deployed across + various Edge Cloud Zones + items: + $ref: "#/components/schemas/ApplicationEndpoint" + applicationProviderName: + type: string + description: Name of the Application Provider + example: "AppProvider" + applicationDescription: + type: string + description: Description of the application. + example: "This is a V2X application." + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + required: + - applicationEndpoints + - applicationProviderName + - applicationProfileId + example: + applicationEndpoints: + - domainName: "app.example.com" + port: 8080 + applicationEndpointDescription: "V2X app deployed at ZoneA" + edgeCloudZone: + edgeCloudZoneId: "123e4567-e89b-12d3-a456-426614174000" + edgeCloudZoneName: "ZoneA" + edgeCloudProvider: "ProviderA" + edgeCloudRegion: "us-west-1" + edgeCloudZoneStatus: "active" + applicationProviderName: "AppProvider" + applicationDescription: "This is a V2X application." + applicationProfileId: "123e4567-e89b-12d3-a456-426614174000" + + ApplicationEndpointList: + type: object + description: | + List of Application endpoints information + deployed across various cloud zones. + required: + - applicationEndpointListId + - applicationEndpointsInfo + properties: + applicationEndpointListId: + $ref: "#/components/schemas/ApplicationEndpointListId" + applicationEndpointsInfo: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + + ApplicationEndpoint: + type: object + description: | + An application server IP address or FQDN with a port, + exposed by an application instance deployed on the Edge Cloud + Zone. + required: + - port + anyOf: + - required: [domainName] + - required: [ipv4Address] + - required: [ipv6Address] + properties: + domainName: + $ref: "#/components/schemas/DomainName" + ipv4Address: + $ref: "#/components/schemas/SingleIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/SingleIpv6Addr" + port: + $ref: "#/components/schemas/Port" + edgeCloudZone: + $ref: "#/components/schemas/EdgeCloudZone" + applicationEndpointDescription: + type: string + description: Description of the application endpoint + example: "V2X app deployed at ZoneA" + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + + EdgeCloudZoneId: + description: A unique identifier for the Edge Cloud Zone. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + EdgeCloudRegion: + description: | + The EdgeCloudProvider's name for the region where the Edge Cloud + Zone is located. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + EdgeCloudProvider: + description: The provider of the Edge Cloud. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ProviderA" + + EdgeCloudZoneName: + description: The name of the Edge Cloud Zone. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ZoneA" + + ApplicationEndpointListId: + description: | + A system-defined string identifier representing + one or more registered Application Endpoints. This ID is generated + by the system upon successful registration of an application and is + used to reference the registered endpoints in subsequent operations. + type: string + format: uuid + readOnly: true + additionalProperties: false + example: "98765432-e89b-12d3-a456-426614174999" + + ApplicationProfileId: + description: | + A unique identifier for the application profile. This represents + the application's network and compute characteristics. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + DomainName: + type: string + description: | + Application's Domain Name, which is a Fully Qualified Domain Name (FQDN). + pattern: ^[a-zA-Z0-9]([a-zA-Z0-9\-]{0,61}[a-zA-Z0-9])?(\.[a-zA-Z0-9]([a-zA-Z0-9\-]{0,61}[a-zA-Z0-9])?)+$ + maxLength: 253 + minLength: 4 + example: "app.example.com" + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + SingleIpv6Addr: + description: | + Single IPv6 address with no subnet mask + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: | + TCP or UDP port number for the application endpoint. + Valid range is 0-65535. + type: integer + minimum: 0 + maximum: 65535 + example: 8080 + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, + request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter + criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions + to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - UNIDENTIFIABLE_APPLICATION_PROFILE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier. + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: Service not supported for this applicationProfileId + UNIDENTIFIABLE_APPLICATION_PROFILE: + description: | + The Application Profile is not included in the request + and the profile information cannot be derived + from the 3-legged access token + value: + status: 422 + code: UNIDENTIFIABLE_APPLICATION_PROFILE + message: The Application Profile cannot be identified + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business + quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to + rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist/raw.md b/marked/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c00d953d113a78849860f38f7d3ecf00904df127 --- /dev/null +++ b/marked/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# Application Endpoints Registration API Readiness minimum criteria checklist + +Checklist for Application-Endpoint-Registration v0.1.0 + +| Nr | API release assets | alpha | release-candidate | initial
    public | stable
    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-endpoint-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/application-endpoint-registration-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-endpoint-registration.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/dAAsC) | diff --git a/marked/ApplicationEndpointRegistration/documentation/API_documentation/README/raw.md b/marked/ApplicationEndpointRegistration/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationEndpointRegistration/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story/raw.md b/marked/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b8b99642351c2ec60edc0da03471712b70d6b1a3 --- /dev/null +++ b/marked/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story/raw.md @@ -0,0 +1,10 @@ +# Application Endpoint Registration API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer who has deployed my application across multiple Edge Cloud Zones, I need a way to register and manage the endpoints of my application instances. The Application Endpoint Registration API allows me to register my application endpoints across different Edge Cloud Zones, update their information when necessary, retrieve endpoint details, and remove endpoints when they are decommissioned. This registration process enables the discovery of these endpoints through the Application Endpoint Discovery API, ensuring users can connect to the optimal instance of my application. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
    **Actors:** Application service providers, hyperscalers, application developers
    **Scope:**
    • Register application endpoints in various Edge Cloud Zones
    • Update existing application endpoint information
    • Retrieve application endpoint details
    • Delete application endpoints when no longer needed
    | +| ***Pre-conditions*** |The preconditions are listed below:
    1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
    2. The API Consumer:BusinessManager has successfully subscribed to the Application Endpoint Registration product from the product catalog.
    3. The API Consumer:Administrator has onboarded the developer:User to the platform.
    4. The API Consumer has deployed application instances across various Edge Cloud Zones and has the necessary information about each endpoint.
    5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.
    | +| ***Activities/Steps*** | **Starts when:**
    1. The API consumer application server makes requests to:
    - Register a new application endpoint by providing endpoint details.
    - Retrieve information about a specific registered endpoint.
    - Update the details of an existing registered endpoint.
    - Delete a registered endpoint that is no longer active.

    **Ends when:**
    1. The API endpoint successfully processes the registration, update, retrieval, or deletion request. | +| ***Post-conditions*** | 1. For registration: A new application endpoint is registered and available for discovery.
    2. For update: The application endpoint information is updated with the latest details.
    3. For retrieval: The current information about the application endpoint is provided.
    4. For deletion: The application endpoint is removed from the registration system and will no longer be discoverable. | +| ***Exceptions*** | Several exceptions might occur
    - Unauthorized: Not valid credentials (e.g. use of already expired access token).
    - Invalid input: Not valid input data to register or update an endpoint (e.g. malformed URI).
    - Conflict: An endpoint with the same identifier already exists during registration.
    - Not Found: The requested endpoint doesn't exist during retrieval, update, or deletion operations. | diff --git a/marked/ApplicationEndpointRegistration/documentation/SupportingDocuments/README/raw.md b/marked/ApplicationEndpointRegistration/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationEndpointRegistration/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ApplicationProfiles/README/raw.md b/marked/ApplicationProfiles/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..30f7c46dc3f53284d793262abe00d08127a74bfa --- /dev/null +++ b/marked/ApplicationProfiles/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationProfiles + +Sandbox API Repository to describe, develop, document, and test the ApplicationProfiles Service API(s) within the context of [ConnectivityInsights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14561833/ConnectivityInsights) + +* API Repository [Wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mgGaBQ) + +## Scope + +* Service API(s) “ApplicationProfiles” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Application profiles allows application developers to share all the information about their application which would be relevant for network CAMARA APIs related decision making. +* Describe, develop, document, and test the API(s) +* Started: October 2024 (within ConnectivityInsights, own repository since March 2025) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationProfiles/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-profiles v0.5.0** + [[YAML]](https://github.com/camaraproject/ApplicationProfiles/blob/r1.2/code/API_definitions/application-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationProfiles/r1.2/code/API_definitions/application-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationProfiles/r1.2/code/API_definitions/application-profiles.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationProfiles/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationProfiles/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationProfiles/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually together with ConnectivityInsights + * Schedule: Bi-weekly on Wednesday at 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vzve) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ApplicationProfiles/code/API_definitions/README/raw.md b/marked/ApplicationProfiles/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/ApplicationProfiles/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/ApplicationProfiles/code/API_definitions/application-profiles/raw.md b/marked/ApplicationProfiles/code/API_definitions/application-profiles/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6393079a9e10867a956a51343b62eca7f1ebc731 --- /dev/null +++ b/marked/ApplicationProfiles/code/API_definitions/application-profiles/raw.md @@ -0,0 +1,687 @@ +# application-profiles + +```yaml +openapi: 3.0.3 +info: + title: Connectivity Insights - Application Profiles + x-camara-commonalities: 0.6 + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + description: | + Application profiles allow developers to specify all relevant information about their application for both network and compute resource + requirements,supporting CAMARA APIs and network decision making. + + This API enables defining, reading, and managing application requirements,including: + - Network quality thresholds (latency, jitter, loss, throughput) + - Compute resource thresholds (CPU, GPU, memory, storage) + + The information captured as part of application profiles can be used in different usecases for decision making. Please refer connectivity insights and session insights for more details as a reference to see how the information in application profiles is used for decision making. + The scope will expand as new requirements from CAMARA APIs emerge. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) for the + released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local + legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + contact: + email: sp-edc@lists.camaraproject.org +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/ApplicationProfiles +servers: + - url: "{apiRoot}/application-profiles/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application Profiles + description: | + Operations to define, read and manage an application's thresholds + for network quality (latency, jitter, loss, throughput) + +paths: + /application-profiles: + post: + security: + - openId: + - application-profiles:create + tags: + - Application Profiles + summary: Create an Application Profile + description: | + Define network monitoring intents for optimal end user application + experience. + operationId: createApplicationProfile + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: List of user-defined network quality thresholds + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfileRequest" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + + /application-profiles/{applicationProfileId}: + patch: + security: + - openId: + - application-profiles:update + tags: + - Application Profiles + summary: Update an Application Profile + description: | + Update the complete set of network quality thresholds for an + application with the new set of thresholds to ensure good + end user experience + operationId: updateApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: | + network monitoring intents for optimal end user application + experience. + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + required: true + responses: + "200": + description: OK + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + get: + security: + - openId: + - application-profiles:read + tags: + - Application Profiles + summary: Get an Application Profile + description: Read an Application Profile + operationId: readApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + delete: + security: + - openId: + - application-profiles:delete + tags: + - Application Profiles + summary: Delete an Application Profile + description: Delete an application profile + operationId: deleteApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Application profile has been deleted successfully. + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + Duration: + type: object + properties: + value: + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + allOf: + - $ref: "#/components/schemas/TimeUnitEnum" + - example: Minutes + + TimeUnitEnum: + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + Rate: + type: object + properties: + value: + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + type: string + enum: + - Bps + - Kbps + - Mbps + - Gbps + - Tbps + + Compute: + type: object + properties: + value: + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/ComputeUnitEnum" + + ComputeUnitEnum: + type: string + enum: + - Kb + - Mb + - Gb + - Tb + + PacketDelayBudget: + description: | + The packet delay budget is the maximum allowable one-way latency + between the customer's device and the gateway from the operator's + network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, + such as voice calls, video streaming, and data. The end-to-end or + round trip latency will be about two times this value plus the latency + not controlled by the operator + allOf: + - $ref: "#/components/schemas/Duration" + + PacketErrorLossRate: + type: integer + description: + The exponential power of the allowable error loss rate 10^(-N). + For instance 3 would be an error loss rate of 10 to the power of -3 + (0.001) + + For 5G network the 3GPP specification TS 23.203 defines the packet + error loss rate QCI attribute. It describes the Quality of Service + (QoS) Class Identifier (QCI) parameters used to differentiate traffic + classes in mobile networks, ensuring appropriate resource + allocation and performance for various services. + + The packet error loss rate is one of the QCI attributes, providing + information on the acceptable packet loss rate for a specific traffic + class. This attribute helps maintain the desired performance level for + services like voice calls, video streaming, or data transfers within + the 3GPP mobile network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + + Jitter: + description: + The jitter requirement aims to limit the maximum variation in + round-trip packet delay for the 99th percentile of traffic, following + ITU Y.1540 standards. It considers only acknowledged packets in a + session, which are packets that receive a confirmation of receipt from + the recipient (e.g., using TCP). This requirement helps maintain + consistent latency, essential for real-time applications such as VoIP, + video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + + TargetMinDownstreamRate: + description: | + This is the target minimum downstream rate. + allOf: + - $ref: "#/components/schemas/Rate" + + TargetMinUpstreamRate: + description: | + This is the target minimum upstream rate. + allOf: + - $ref: "#/components/schemas/Rate" + + targetMinCPU: + type: number + description: + Number of vCPUs required for the application. Fractional values are allowed (e.g., 0.5 = half a vCPU). The value represents the minimum amount of CPU resources to be allocated to the application instance. + example: 0.5 + + targetMinGPU: + description: | + This is the target minimun GPUs required by the application + format: integer + example: 1 + + gpuVendorType: + type: string + enum: + - Nvidia + - AMD + description: GPU vendor name e.g. NVIDIA, AMD etc. + example: Nvidia + + gpuModelName: + type: string + description: Model name corresponding to vendorType may include info e.g. for NVIDIA, model name could be “Tesla M60”, “Tesla V100” etc. + + targetMinMemory: + description: | + This is the target minimum memory required by the application + allOf: + - $ref: "#/components/schemas/Compute" + + targetMinEphemeralStorage: + description: | + This is the target minimum ephemeral storage required by the application + allOf: + - $ref: "#/components/schemas/Compute" + + targetMinPersistentStorage: + description: | + This is the target minimum persistent storage required by the + application + allOf: + - $ref: "#/components/schemas/Compute" + + ApplicationProfile: + type: object + required: + - applicationProfileId + properties: + applicationProfileId: + type: string + format: uuid + networkQualityThresholds: + $ref: "#/components/schemas/NetworkQualityThresholds" + computeResources: + $ref: "#/components/schemas/ComputeResourcesThresholds" + anyOf: + - required: [networkQualityThresholds] + - required: [computeResources] + + ApplicationProfileRequest: + type: object + anyOf: + - required: [networkQualityThresholds] + - required: [computeResources] + properties: + networkQualityThresholds: + $ref: "#/components/schemas/NetworkQualityThresholds" + computeResources: + $ref: "#/components/schemas/ComputeResourcesThresholds" + + NetworkQualityThresholds: + type: object + properties: + packetDelayBudget: + $ref: "#/components/schemas/PacketDelayBudget" + targetMinDownstreamRate: + $ref: "#/components/schemas/TargetMinDownstreamRate" + targetMinUpstreamRate: + $ref: "#/components/schemas/TargetMinUpstreamRate" + packetLossErrorRate: + $ref: "#/components/schemas/PacketErrorLossRate" + jitter: + $ref: "#/components/schemas/Jitter" + minProperties: 1 + + ComputeResourcesThresholds: + type: object + properties: + targetMinCPU: + $ref: "#/components/schemas/targetMinCPU" + targetMinMemory: + $ref: "#/components/schemas/targetMinMemory" + gpuVendorType: + $ref: "#/components/schemas/gpuVendorType" + gpuModelName: + $ref: "#/components/schemas/gpuModelName" + targetMinGPU: + $ref: "#/components/schemas/targetMinGPU" + targetMinGPUMemory: + $ref: "#/components/schemas/targetMinMemory" + targetMinEphemeralStorage: + $ref: "#/components/schemas/targetMinEphemeralStorage" + targetMinPersistentStorage: + $ref: "#/components/schemas/targetMinPersistentStorage" + description: Compute resources of a Application Profile + minProperties: 1 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body + or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when + a given field has a pre-defined range or a invalid filter + criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not + have the required scope or when the user fails operational + security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business + quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due + to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/ApplicationProfiles/documentation/API_documentation/README/raw.md b/marked/ApplicationProfiles/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationProfiles/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist/raw.md b/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..12ee979d4fbc6459c66cb27bd482bb298b1a47e0 --- /dev/null +++ b/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for application-profiles v0.5.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
    public | stable
    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/application-profiles-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-profiles.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/iQFmBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story/raw.md b/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5f9ee8b2f219bf946fccc3d9ba2cdbc6834e5510 --- /dev/null +++ b/marked/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story/raw.md @@ -0,0 +1,10 @@ +# Application profiles API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to share key details about my application that are relevant for network-related decisions across various CAMARA APIs. Specifically, I need to define, store, and manage my application's network quality thresholds (latency, jitter, packet loss, and throughput) that represent my application's networking demands. These thresholds will serve as a baseline for determining whether the network can provide adequate performance for my application's users | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
    **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
    **Scope:**
    • Create and manage application profiles
    • Perform network quality check againt the application profile for specific user sessions
    • Create subscriptions to recieve notifications if the network is not able to meet the application's requirements
    | +| ***Pre-conditions*** |The preconditions are listed below:
    1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
    2. The API Consumer:BusinessManager has successfully subscribed to the Application Profiles product from the product catalog.
    3. The API Consumer:Administrator has onboarded the developer:User to the platform.
    4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
    5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:**
      1. The API consumer makes a POST request to /application-profiles with network quality thresholds including packetDelayBudget, targetMinDownstreamRate, targetMinUpstreamRate, packetlossErrorRate, and jitter.

      **Additional Operatios:**
      2. The API consumer can make a GET request to /application-profiles/{applicationProfileId} to retrieve an existing profile.
      3. The API consumer can make a PATCH request to /application-profiles/{applicationProfileId} to update network quality thresholds for an existing profile.
      4. The API consumer can make a DELETE request to /application-profiles/{applicationProfileId} to remove a profile that is no longer needed.

      **Ends when:**
      The application profile is either successfully created, updated, retrieved, or deleted based on the API consumer's request. | +| ***Post-conditions*** | 1. For POST: A new application profile is created with a unique applicationProfileId and the specified network quality thresholds.
      2. For GET: The details of the requested application profile are returned to the API consumer.
      3. For PATCH: The application profile is updated with the new network quality thresholds.
      4. For DELETE: The application profile is removed from the system.| +| ***Exceptions*** | Several exceptions might occur
      - Bad Request: Invalid argument or out-of-range values for network quality thresholds.
      - Unauthorized: Invalid, missing, or expired access token.
      - Forbidden: Insufficient permissions or invalid token context.
      - Not Found: Requested application profile does not exist.
      - Too Many Requests: Rate limit or quota exceeded.| diff --git a/marked/ApplicationProfiles/documentation/SupportingDocuments/README/raw.md b/marked/ApplicationProfiles/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ApplicationProfiles/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/BlockchainPublicAddress/README/raw.md b/marked/BlockchainPublicAddress/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..412e131692dfc09558c26b80cc2b0e60c6124f14 --- /dev/null +++ b/marked/BlockchainPublicAddress/README/raw.md @@ -0,0 +1,58 @@ + + + + + + + + + +# BlockchainPublicAddress + +Sandbox API Repository to describe, develop, document, and test the BlockchainPublicAddress Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KDHe) + +## Scope +* Service APIs for “Blockchain Public Address” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Blockchain Public Address API: + * Manage a Blockchain Public Address associated to a phone number, i.e. to retrieve the blockchain public address(es) and to bind/unbind a Blockchain Public Address. The Blockchain Public Address is utilized as Decentralized Identifier (DID). With the proposed API, API providers offer API consumers the following capability: pairing phone number with Blockchain Public Address whenever this 3rd party wants to offer its customers a way to make transactions more easily based on the phone number instead of the Blockchain Public Address. + * Optional binding enforcement procedure, ensuring both `phoneNumber` and `blockchainPublicAddress` belongs to the same owner (i.e. person), within binding process by means of the checking of provided `nonce` and `signature` fields. To generate `nonce` below mentioned Blockchain Public Address Validation API has been designed, and `signature` generation is an off-chain process. + * Blockchain Public Address Validation API: + * Manage generation of a nonce (one-time challenge) to be used in binding enforcemnet procedure. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: June 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/r2.2) (Fall25), with the following API versions: + * **blockchain-public-address-validation v0.1.0** + [[YAML]](https://github.com/camaraproject/BlockchainPublicAddress/blob/r2.2/code/API_definitions/blockchain-public-address-validation.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address-validation.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address-validation.yaml) + * **blockchain-public-address v0.3.0** + [[YAML]](https://github.com/camaraproject/BlockchainPublicAddress/blob/r2.2/code/API_definitions/blockchain-public-address.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address.yaml) +* The latest public release is always available here: https://github.com/camaraproject/BlockchainPublicAddress/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/BlockchainPublicAddress/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99023344259?password=cb995600-56ee-48a2-ade1-607bb10487df) + * Schedule: Bi-weekly on Thursdays, 13:00-14:00 CET/CEST (12:00 UTC, 11:00 UTC during European DST) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/thDe). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation/raw.md b/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6dafe7fc65f484c24de1985b2d636aee58dd8ce0 --- /dev/null +++ b/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation/raw.md @@ -0,0 +1,258 @@ +# blockchain-public-address-validation + +```yaml +openapi: 3.0.3 +info: + title: Blockchain Public Address Validation + description: |- + This API allows the API consumer to generate a one-time nonce for Enhanced Binding validation for Blockchain Public Address associated with a mobile phone number. + + # Relevant Definitions and concepts + - **Blockchain Public Address**: Unique string of code used by individuals that can be used to send, receive, and store digital assets (e.g. payments in cryptocurrencies, smart contracts, NFT (Non-Fungible Tokens), etc.) on a blockchain network + to receive or request payments in cryptocurrency. + + # API Functionality + This API allows to generate a one-time nonce to allow for enhanced validation procedure for Blockchain Public Address binding associated with a mobile phone number, as per defined in `bindBlockchainPublicAddress` operation of CAMARA Blockchain Public Address API. + + # Resources and Operations overview + This API provides one endpoint: + - **Endpoint to generate a one-time nonce associated to a specific Blockchain Public Address**. It does not matter if the mobile phone number is already bound to a Blockchain Public Address, as this operation adds a new Blockchain Public Address. This operation MUST be used with a 3-legged Access Token + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further Info and Support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/BlockchainPublicAddress +servers: + - url: "{apiRoot}/blockchain-public-address-validation/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Blockchain Public Address Validation Nonce + description: API operations to manage Blockchain Public Address Validation Nonce +paths: + /nonce: + post: + tags: + - Blockchain Public Address Validation Nonce + summary: Generates a one-time nonce associated to a specific Blockchain Public Address + description: Generates a one-time nonce (i.e. challenge) associated to a specific Blockchain Public Address to allow for enhanced validation as per defined in `bindBlockchainPublicAddress` operation of CAMARA Blockchain Public Address API. + operationId: createBlockchainPublicAddressValidationNonce + security: + - openId: + - blockchain-public-address-validation:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBlockchainPublicAddressValidationNonce" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBlockchainPublicAddressValidationNonceResponse" + examples: + CreateBlockchainPublicAddressValidationNonceResponse201Example: + value: + nonce: "abc626ce-5284-4a84-b85e-46e0ee3d0434" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreateBlockchainPublicAddressValidationNonce: + type: object + description: Payload to request the nonce generation associated to a given Blockchain Public Address + required: + - blockchainPublicAddress + properties: + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address use for the latter binding to a specific `phoneNumber`. + example: + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + CreateBlockchainPublicAddressValidationNonceResponse: + type: object + description: Nonce generation associated to a given Blockchain Public Address response + required: + - nonce + properties: + nonce: + type: string + description: |- + One-time challenge generated associated to indicated `blockchainPublicAddress`. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address/raw.md b/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..64aa6058088dfcca2a314830a14880a5c04e33b3 --- /dev/null +++ b/marked/BlockchainPublicAddress/code/API_definitions/blockchain-public-address/raw.md @@ -0,0 +1,663 @@ +# blockchain-public-address + +```yaml +openapi: 3.0.3 +info: + title: Blockchain Public Address + description: |- + This API allows the API consumer to manage Blockchain Public Address associated with a mobile phone number. + + # Relevant Definitions and concepts + - **Blockchain Public Address**: Unique string of code used by individuals that can be used to send, receive, and store digital assets (e.g. payments in cryptocurrencies, smart contracts, NFT (Non-Fungible Tokens), etc.) on a blockchain network + to receive or request payments in cryptocurrency. + + # API Functionality + This API allows the API consumer to manage a Blockchain Public Address associated with a mobile phone number, i.e.: to retrieve the Blockchain Public Address(es) and to bind/unbind a Blockchain Public Address. + + # Resources and Operations overview + This API provides three endpoints: + - **Endpoint to retrieve the Blockchain Public Address(es) associated with a mobile phone number sent as input**. The Blockchain Public Address is information made available by the user, in association to their mobile phone number. Then, this endpoint may be accessed in 2-legged or in 3-legged mode. Even in 3-legged mode, the mobile phone number included as input field does not need to belong to the `sub` (representing the User) for which the Access Token is issued. This will enable a user to ask for the Blockchain Public Address(es) of any mobile phone number, in order to perform a transaction with one of the available ones (send or request). + - **Endpoint to associate a mobile phone number with a Blockchain Public Address**. It does not matter if the mobile phone number is already bound to a Blockchain Public Address, as this operation adds a new Blockchain Public Address. This operation MUST be used with a 3-legged Access Token, and the indicated mobile phone number must belong to the `sub` (representing the User) in the Access Token; this is because only the user of the mobile phone number must be able to perform a bind. As a consequence, this operation will only work with mobile phone numbers of the Telco Operator exposing the API. + - **Endpoint to remove the association of a mobile phone number with a Blockchain Public Address**. This operation MUST be used with a 3-legged Access Token; this is because only the user of the mobile phone number must be able to perform an unbind. Note: Due to this, the API Server must validate that the `id` included in the request refers to a bind for a mobile phone number belonging to the `sub` (representing the User) in the Access Token. As a consequence, this operation will only work with mobile phone numbers of the Telco Operator exposing the API. + + ## Enforcement of the Blockchain Public Address ownership in binding process + + The enforcement of the Blockchain Public Address ownership in the binding process is optional, and it is not mandatory to use the `nonce` and `signature` fields. If the API consumer does not want to enforce this, it can simply omit these fields in the request body. + + This enforcement is aimed to ensure that the Blockchain Public Address being bound to a mobile phone number is indeed owned by the user (i.e. person behind) of that mobile phone number. + The API consumer can request the user to sign a `nonce` off-chain, and then include the `nonce` and `signature` in the request body when binding the Blockchain Public Address. The API Server will then verify that the `signature` is valid for the given `nonce` and `blockchainPublicAddress`. + + The E2E procedure is depicted in below picture: + ![Binding Enforcement - Off-Chain Signature](https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/documentation/API_documentation/resources/blockchain-public-address-binding-enforcement-off-chain-signature.png) + + LEGEND: + - `API Server`, `Challenge Module` and `Binding Database` are functional components that represent the underlying Backend API Logic in the Telco Operator. How this CAMARA API is implemented by a Telco Operator is out of scope of this specification. + + It comprises four steps: + - **(A) Obtain 3-Legged Access Token**: This is the regular process of obtaining a CAMARA 3-legged Access Token. CAMARA OIDC Authorization Code Flow is mentioned for illustrative purposes, other CAMARA 3-legged Access Token flows may be used. Check CAMARA Identity and Consent Management WG for details. + - **(B) Request a nonce from the API Server**: This is the feature provided by **_CAMARA Blockchain Public Address Validation Nonce API_**, allowing the API consumer to request a `nonce` associated to the `blockchainPublicAddress` to be signed by the user. + - **(C) Ask the user to sign the nonce off-chain**: The API consumer will use this `nonce` to ask the user to sign it off-chain. The user will sign the `nonce` using their private key. The API consumer will then obtain a `signature`, which is a cryptographic proof that the user owns the `blockchainPublicAddress`. + - **(D) Bind the Blockchain Public Address to the mobile phone number**: This step includes the `nonce` and `signature` in the request body. For signature validation, there are many options (e.g. https://ecrecover.org/, tools like `ethers.js` or `web3.js`); that is an implementation topic out of scope of this CAMARA API specification. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further Info and Support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/BlockchainPublicAddress +servers: + - url: "{apiRoot}/blockchain-public-address/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Blockchain Public Address + description: API operations to manage Blockchain Public Addresses +paths: + /blockchain-public-addresses/retrieve-blockchains: + post: + tags: + - Blockchain Public Address + summary: Retrieves Blockchain Public Address associated with a mobile phone number. + description: + Retrieves Blockchain Public Address associated with a mobile phone number. This operation can be accessed in 3-legged and in 2-legged, notice that the mobile phone number used as input need not be related with the user or mobile phone number to which the Access + Token is associated; this is because the operation is intended to be used to manage Blockchain Public Address of any mobile phone number, in order to perform send or request crypto operations. + operationId: retrieveBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + description: Array of Blockchain Public Addresses bound to the mobile phone number + items: + $ref: "#/components/schemas/BlockchainPublicAddressResponse" + examples: + RetrieveBlockchainPublicAddressResponse200Example: + value: + - id: "90c626ce-5284-4a84-b85e-46e0ee3d0434" + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + blockchainNetworkId: "evm:1" + currency: + - ETH + - id: "5c179f50-db37-4d23-87e3-6f10c991899f" + blockchainPublicAddress: "0x329CdCAAC31c934fe32322b111bE8fBd30b4FFA9" + blockchainNetworkId: "evm:137" + currency: + - WETH + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /blockchain-public-addresses: + post: + tags: + - Blockchain Public Address + summary: Binds Blockchain Public Address to a mobile phone number + description: + Binds Blockchain Public Address to a mobile phone number. If the mobile phone number is already bound to a Blockchain Public Address, this operation will add a new bound Blockchain Public Address to the mobile phone number. This operation is intended to be used + with a 3-legged Access Token, and the indicated mobile phone number must belong to the user identified by its `sub` in the Access Token; this is because only the user of the mobile phone number must be able to perform the bind. + + Specifically for this functionality, when a binding operation indicates a `blockchainNetworkId` not allowed by Telco Operator exception `403 - BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED` will be generated. + operationId: bindBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/BindBlockchainPublicAddressRequest" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BindBlockchainPublicAddressResponse" + examples: + BindBlockchainPublicAddressResponse201Example: + value: + id: "90c626ce-5284-4a84-b85e-46e0ee3d0434" + "400": + $ref: "#/components/responses/InvalidArgumentForBlockchain400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PermissionDeniedForBlockchain403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /blockchain-public-addresses/{id}: + delete: + tags: + - Blockchain Public Address + summary: Unbinds Blockchain Public Address association to a mobile phone number + description: |- + Unbinds Blockchain Public Address to a mobile phone number. This operation is intended to be used with a 3-legged Access Token; this is because only the user of the mobile phone number must be able to perform the unbind. + Note: Due to this, the API Server must validate that the `id` included in the request refers to a bind for a mobile phone number belonging to the user identified by its `sub` in the Access Token. + operationId: deleteBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:delete + parameters: + - $ref: "#/components/parameters/Id" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: No Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Id: + name: id + in: path + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + required: true + schema: + type: string + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: object + description: Payload to retrieve the Blockchain Public Address(es) associated to a given Phone Number + required: + - phoneNumber + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + BindBlockchainPublicAddressRequest: + type: object + description: Payload to request the Bind of the Blockchain Public Address + required: + - phoneNumber + - blockchainPublicAddress + - blockchainNetworkId + properties: + phoneNumber: + type: string + description: Mobile phone number to which the Blockchain Public Address will be bound. A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address to bind to the mobile `phoneNumber` + blockchainNetworkId: + type: string + pattern: ^[a-zA-Z0-9]+:?[a-zA-Z0-9]+$ + description: |- + Identifier (i.e. name/type) of the blockchain whose address value is provided within `blockchainPublicAddress`. The model proposed aims to provide an extensible way to list/identify every blockchain ecosystems. + Proposed format is: `:`, where: + + - ``: Represents a Layer 1 Blockchain Ecosystem (e.g. ethereum, bitcoin,...) + - ``: Represents subsequents L2 and Testnet Blockchain Ecosystems, whenever they apply (e.g. bitcoin is a monolithic blockchain so as this concept does not apply) + + So far, in the scope of v0.2 of this specification, the following `` values are covered: + - `evm`: Representing a common L1 Layer concept for EVM-based networks. Within this Ecosystem, `` concept is required and matches the value of chainId as per [EVM ChainId](https://chainid.network/). For instance: + - `ethereum` blockchain would be identified by `evm:1` value (i.e. ethereum mainnet). + - `polygon` blockchain would be identified by `evm:137` value (i.e. polygon mainnet). + - `celo` blockchain would be identified by `evm:42220` value (i.e. celo mainnet). + - `aleph zero` blockchain would be identified by `evm:41455` value (i.e. aleph zero evm). + - `bitcoin`: Representing Bitcoin L1 blockchain. No `` concept applies for this L1 Ecosystem + - `solana`: Representing Solana L1 blockchain. No `` concept applies for this L1 Ecosystem + - `cardano`: Representing Cardano L1 blockchain. No `` concept applies for this L1 Ecosystem + currency: + type: array + description: List of currencies for the blockchain. Optional field (generally not needed), only indicated when there are business needs to set one or a list on currencies supported. + minItems: 0 + items: + type: string + nonce: + type: string + description: |- + One-time challenge generated by means of endpoint `createBlockchainPublicAddressValidationNonce` of CAMARA API Blockchain Public Address Challenge. + + It is used along with `signature` to perform optional enhanced enforcement to ensure blockChainPublicAddress can be associated to the phoneNumber as it belongs to the owner of the blockChainPublicAddress. + signature: + type: string + description: |- + Unique distinctive generated as a result of asking the user to sign the nonce off-chain. + + It is used along with `nonce` to perform optional enhanced enforcement to ensure blockChainPublicAddress can be associated to the the phoneNumber as it belongs to the owner of the blockChainPublicAddress. + example: + phoneNumber: "+346789990012" + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + blockchainNetworkId: "evm:1" + currency: + - ETH + BindBlockchainPublicAddressResponse: + type: object + description: Bind Blockchain Public Address response + required: + - id + properties: + id: + type: string + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + BlockchainPublicAddressResponse: + type: object + description: Blockchain Public Address response + required: + - id + - blockchainPublicAddress + - blockchainNetworkId + properties: + id: + type: string + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address + blockchainNetworkId: + type: string + description: |- + Identifier (i.e. name/type) of the blockchain whose address value is provided within `blockchainPublicAddress`. The model proposed aims to provide an extensible way to list/identify every blockchain ecosystems. + Proposed format is: `:`, where: + - ``: Represents a Layer 1 Blockchain Ecosystem (e.g. ethereum, bitcoin,...) + - ``: Represents subsequents L2 and Testnet Blockchain Ecosystems, whenever they apply (e.g. bitcoin is a monolithic blockchain so as this concept does not apply) + + So far, in the scope of v0.2 of this specification, the following `` values are covered: + - `evm`: Representing a common L1 Layer concept for EVM-based networks. Within this Ecosystem, `` concept is required and matches the value of chainId as per [EVM ChainId](https://chainid.network/). For instance: + - `ethereum` blockchain would be identified by `evm:1` value (i.e. ethereum mainnet). + - `polygon` blockchain would be identified by `evm:137` value (i.e. polygon mainnet). + - `celo` blockchain would be identified by `evm:42220` value (i.e. celo mainnet). + - `aleph zero` blockchain would be identified by `evm:41455` value (i.e. aleph zero evm). + - `bitcoin`: Representing Bitcoin L1 blockchain. No `` concept applies for this L1 Ecosystem + - `solana`: Representing Solana L1 blockchain. No `` concept applies for this L1 Ecosystem + - `cardano`: Representing Cardano L1 blockchain. No `` concept applies for this L1 Ecosystem + currency: + type: array + description: List of currencies for the blockchain. Optional field (generally not needed), only indicated when there are business needs to set one or a list on currencies supported. + minItems: 0 + items: + type: string + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + InvalidArgumentForBlockchain400: + description: | + Problem with the client request. + In addition to regular scenario of INVALID_ARGUMENT, other exceptions may exist. + - Indicated blockchainNetworkId is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER","message": "Indicated blockchainNetworkId is not valid") + - Indicated currency is not valid for the Blockchain ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY","message": "Indicated currency is not found") + - Currency indication is required ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED","message": "One currency is required") + - Indicated nonce is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE","message": "Indicated nonce is not valid") + - Indicated signature is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE","message": "Indicated signature is not valid") + - Both nonce and signature are required together to perform enhanced validation ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED","message": "Both nonce and signature are required for enhanced validation") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY + - BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE + - BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_BLOCKCHAIN_NETWORK_ID: + description: blockchainNetworkId is not valid + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER + message: Indicated blockchainNetworkId is not valid + GENERIC_400_INVALID_CURRENCY_FOR_BLOCKCHAIN: + description: Invalid currency + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY + message: Indicated currency is not found + GENERIC_400_REQUIRED_CURRENCY_FOR_BLOCKCHAIN: + description: Currency is required + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED + message: One currency is required + GENERIC_400_INVALID_NONCE: + description: Invalid nonce + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE + message: Indicated nonce is not valid + GENERIC_400_INVALID_SIGNATURE: + description: Invalid signature + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE + message: Indicated signature is not valid + GENERIC_400_BOTH_NONCE_SIGNATURE_REQUIRED: + description: Both nonce and signature are required together + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED + message: Both nonce and signature are required for enhanced validation + PermissionDeniedForBlockchain403: + description: | + Forbidden. + In addition to regular scenario of PERMISSION_DENIED, other exceptions may exist. + - Blockchain identifier not allowed by business rules ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED","message": "Indicated blockchainNetworkId is not allowed by business rules") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_NOT_ALLOWED_BLOCKCHAIN_NETWORK_ID: + description: blockchainNetworkId not allowed by business rules + value: + status: 403 + code: BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED + message: Indicated blockchainNetworkId is not allowed by business rules + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic422: + description: |- + Unprocessable content. + - Enhanced Binding validation procedure by means of nonce and signature verification is not supported ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION","message": "Enhanced Binding validation procedure is not supported") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION + examples: + GENERIC_422_UNSUPPORTED_ENHANCED_VALIDATION: + description: Enhanced Binding validation procedure by means of nonce and signature verification is not supported + value: + status: 422 + code: BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION + message: Enhanced Binding validation procedure is not supported + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist/raw.md b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..94ef1cdaf8fb2024e7b7def8d4eae6ca00f5aaa3 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for BlockChain Public Address v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/blockchain-public-address-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/noDWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story/raw.md b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f347ae84d52e015717159abedbb04d9e4667b58f --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story/raw.md @@ -0,0 +1,26 @@ +# BlockchainPublicAddress API User Stories + +| **Item** | **Details** | +| ---------- | ------------- | +| **US#1** | User Story #1 | +| ***Summary*** | As an application developer, I want a feature to fetch Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain. This way management of Blockchain Public Addresses can be perfomed by means of the phoneNumber, which is a natural concept within the OBs. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** Obtain Blockchain Public Addresses associated to a given phoneNumber of the Customer | +| ***Pre-conditions*** | N/A | +| ***Activities/Steps*** | **Starts when:** The API Consumer makes a GET request to the Blockchain Public Address API to obtain the Blockchain Public Addresses associated to a given phoneNumber (generally such addresses are identified by a DID (Decentralised Identifier, which indeed is a public address of a blockchain), composed of 26-35 alphanumeric characters in length).
      **Ends when:** The API Consumer receives GET response with the list of Blockchain Public Addresses associated to the phoneNumber, including this information:
      - Blockchain public address name.
      - Blockchain public address identifier (DID).
      - Blockchain public address identifier binding (for latter management).
      - Blockchain public address currency.
      Empty response will be received in case no Blockchain Public Address is linked to the phonNumber yet. | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address(es) retrieval linked to a given phoneNumber
      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
      - Invalid Argument: Not valid phoneNumber.
      - Internal: Server Error when fetching information. | +| -------- | ------------- | +| **US#2** | User Story #2 | +| ***Summary*** | As an application developer, I want a feature to manage (bind/unbind) Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** Manage Blockchain Public Addresses binding/unbinding them to a given phoneNumber of the Customer | +| ***Pre-conditions*** | Blockchain Public Address exists in advance | +| ***Activities/Steps*** | **BINDING PROCESS**
      **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address API to bind a specific Blockchain Public Addresses to a provided phoneNumber.
      **Ends when:** The API Consumer receives POST response with this unique binding identifier.

      **UNBINDING PROCESS**
      **Starts when:** The API Consumer makes a DELETE request to the Blockchain Public Address API to unbind a specific Blockchain Public Addresses - phoneNumber relationship, providing the binding identifier that identifies such relationship.
      **Ends when:** The API Consumer receives DELETE response indicating a successful process performed (i.e. deletion). | +| ***Post-conditions*** | **BINDING PROCESS**
      Binding relationship between Blockchain Public Address and phoneNumber is created. If making GET request an item showing that binding is included.

      **UNBINDING PROCESS**
      Binding relationship between Blockchain Public Address and phoneNumber is deleted. If making GET request the item showing that binding is no longer included. | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address management

      **BINDING PROCESS**
      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
      - Invalid Argument: Not valid phoneNumber and/or BlockChain Public Address Information.
      - Internal: Server Error when fetching information.

      **UNBINDING PROCESS**
      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
      - Invalid Argument: Not valid binding identifier.
      - Internal: Server Error when fetching information. | +| **US#3** | User Story #3 | +| ***Summary*** | As an application developer, I want a feature to manage bind Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain, and also performing Binding Enforcement by ensuring the phoneNumber and the blockchainPublicAddress belongs to the same owner | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** Manage Blockchain Public Addresses binding to a given phoneNumber of the Customer with Binding enforcement feature requested | +| ***Pre-conditions*** | Blockchain Public Address exists in advance | +| ***Activities/Steps*** | **BINDING PROCESS**
      **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address API to bind a specific Blockchain Public Addresses to a provided phoneNumber, also indicating the nonce and signature fields.
      **Ends when:** The API Consumer receives POST response with this unique binding identifier. | +| ***Post-conditions*** | **BINDING PROCESS**
      Binding relationship between Blockchain Public Address and phoneNumber is created. If making GET request an item showing that binding is included. | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address management

      **BINDING PROCESS**
      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
      - Invalid Argument: Not valid phoneNumber, BlockChain Public Address, nonce or signature Information.
      - Internal: Server Error when fetching information. | \ No newline at end of file diff --git a/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist/raw.md b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..83cdd09a6c22409aaa0d284806a7e02d4a5c867a --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for BlockChain Public Address Validation v0.1.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address-validation.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address-validation.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/blockchain-public-address-validation-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYASD) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story/raw.md b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9979b75ba3714f79a024ed5fb19846bae4f3a5f0 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story/raw.md @@ -0,0 +1,11 @@ +# BlockchainPublicAddress Validation API User Stories + +| **Item** | **Details** | +| ---------- | ------------- | +| **US#1** | User Story #1 | +| ***Summary*** | As an application developer, I want a feature to generate a nonce (one-time challenge) associated to a blockchain public address, in order for the customer to be able to sign it off-chain, generating a signature. This will allow afterwards to perform binding enforment via Blockchain Public Address binding process. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** Obtain a nonce associated to a blockchainPublicAdress of the Customer | +| ***Pre-conditions*** | N/A | +| ***Activities/Steps*** | **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address Validation API to obtain a nonce associated to a blockchainPublicAdress (indicated as an input) of the Customer.
      **Ends when:** The API Consumer receives POST response with the nonce value. | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the nonce generation
      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
      - Invalid Argument: Not valid blockchainPublicAddress.
      - Internal: Server Error when fetching information. | diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..97d1aaf4dd5d5ee4d39a7aaa086e413016dd269a --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06/raw.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-jul-2023
      +**Status:** FINAL + + +## Attendees +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jose Antonio Ordoñez Lucena (Telefonica) +- Pedro Díez (Telefonica) + + +## Goals +WG Kick-Off Meeting
      + + +Item | Who | Description +---- | ---- | ---- +Members Presentation | WG | Members Presentation +[Issue#2](https://github.com/camaraproject/BlockchainPublicAddress/issues/2) | Telefonica | Kick-Off 6th July +[Issue#3](https://github.com/camaraproject/BlockchainPublicAddress/issues/3) | Telefonica | Initial Use Cases Proposal +[PR#4](https://github.com/camaraproject/BlockchainPublicAddress/pull/4) | Telefonica | BlockChain Use Cases +[Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6) | Telefonica | Baseline Proposal +[PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Telefonica | Baseline Proposal (API YAML Code) + + +### Items Discussion + +Item | Discussion +---- | ---- +Members Presentation | Attendees from Deustche Telekom, Vodafone and Telefonica introduce themselves. +[Issue#2](https://github.com/camaraproject/BlockchainPublicAddress/issues/2) | Introduced by Telefonica. Compiles the agenda for Kick-Off meeting points:
      • Meetings schedule: Agreed to have, in a bi-weekly basis, on Thursdays 13:00 - 14:00 CET/CEST
      • Kind request for Maintainers and Codeowners. Explained the roles and provided more info offline. As tentative candidates we have: Klaus (VF) and Georgios (DT) for maintainers; Klaus (VF) and Krzysztof (DT) for codeowners. To be confirmed in the next days.
      • Presenting initial proposal in the following item. +[Issue#3](https://github.com/camaraproject/BlockchainPublicAddress/issues/3), [PR#4](https://github.com/camaraproject/BlockchainPublicAddress/pull/4) | Presented Use Cases proposal, based on the rationale of providing some features to third parties to be able to manage Blockchains from end users via the phone numbers of the users. Features to fetch blockchain public addresses per phone number and to bind/unbind a Blockchain to/from a phone number.
      • Comments raised by DT and VF that proposal is needed to be enhanced based on WG output in order to have some mentioned regarding AuthN/AuthZ and privacy considerations +[Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Going through the Baseline API definition. Explaining the endpoints:
      - Endpoint to fetch blockchain public addresses linked for a given phoneNumber
      - Endpoint to bind a blockchain public address to a phoneNumber
      - Endpoint to unbind a blockhain public address <-> phoneNumber
      Rationale/Background of the proposal in this [PR-WG#154](https://github.com/camaraproject/WorkingGroups/pull/154)

      Main comments provided:
      • Vodafone: Concerns about the use of DID as blockchain identifier as other standards/identifiers also could be used. Also comments about AuthN/AuthZ model for this API.

      • Deutsche Telekom: Need to work in AuthN/AuthZ model for this API as well as management of User Consent. DT indicated their concern about using the phone number of the user to have such an association. Also DT provided during the meeting information about other forums where work about blockchain is being made:
      - https://github.com/ChainAgnostic/CASA
      - https://chainagnostic.org/
      - https://chainagnostic.org/CAIPs/caip-2
      - https://github.com/UCRegistry/chain-registry

      • Telefonica commented that they are good comments to start and bear in mind; also regarding consents that there is a WG (Identity and Consent Management) where this kind of topics are been addressed. + + +### Next Steps +- Next Meetings:
      + • 20th July - 13:00 - 14:00 CEST
      + • 27th July - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cd0e9c9fae00f6ce34551ac27c624edbe9cbdde4 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes + +## Meeting Information +**Meeting Date:** 20-jul-2023
      +**Status:** FINAL + + +## Attendees +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals + +Review Members Access to WG
      +Next Actions
      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG | WG | Check susbcription status of members +Next Actions | WG | Actions for next meeting + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG | Commented in the meeting, in order to be able to manage maintainers and code owners for the WG. Being checked by VF members (Sebastian, Klaus). Sebastian seems to have access, Klaus is managing it. Issue will be opened when members have access to WG in order to include them as maintainers/codeowners based on their github user. +Next Actions | Commented about the following:
      • Adopting github templates as per Commonalities. To be more agile, Rafał (DT) will generate PR so it can be reviewed and merged (currently only Pedro as codeowner) [PR#8](https://github.com/camaraproject/BlockchainPublicAddress/pull/8). Generated after meeting. Reviewed and Merged.

      • Blockchain identification: Use of a DID is to ensure the "user identification" within a blockchain. The fact of binding it to a phoneNumber is to make a friendly way for Devs and Users to manage transactions between blockchains in a more natural way.

      • Comments raised by VF in order to provide more detail in Use Cases. Deeping into access to the functionality and privacy topics. Issue to be opened by TEF in order to provide information and begin discussion (that can be lead into Use Cases description enhancements and API spec adjustments).

      • Question raised by VF within [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6) about the need of indicating a currency in binding and fetch blockchain functionality. Within a given blockchain, several currencies may be used, so it might not be considered as mandatory in design. Also, Use Cases can guide in the inclusion of this metainformation. TEF will also check internally this. + + +### Next Steps + +- Next Meetings:
      +• 27th July - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ddea724dc345f10248b99855f5be968e1fca2113 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27/raw.md @@ -0,0 +1,46 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 27-jul-2023
      +**Status:** FINAL + + + +## Attendees + +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Georgios Papadopoulos (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
      +Open Issues
      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Sebastian (VF) already has access to WG. Klaus (VF) is managing it. Georgios (DT) will manage it. After that, PR will be generated to indicate maintainers and codeowners. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Telefonica provides more info about Use Cases. Vodafone comments the topic of how to manage the consent of accessing the information (GET List of Blockchains of a given phonenumber). If this endpoint can be accessed vía 2-legged how this access can be controlled in a way the user's phone owner can control the list of people they can view his blockchain addresses. Several initial options commented during the meeting (functionality to have whitelist option where indicate phonenumbers that can access blockchain of other phone numbers, hashing of blockchain and/or phone number). Need to have more discussion around the issue. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Issue opened to reflect the point raised by Vodafone regarding 'currency' as mandatory parameter. Vodafone indicates there are many use cases (e.g. smart contract tokens) where transactions within the same blockchain can be performed with different currencies. Deutsche Telekom also agrees on that. Telefonica needs to check internally (mentioned that initial proposal was to consider one currency but open to cover also other scenarios). TEF will provide feedback and proposal about this topic. +AoB | Control of rate limit of requests, commented by Deustche Telekom. To have some rate control policy in Telco Operator API GW, needed to cover it in API design. There is some exception defined in commonalities: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md#32-http-response-codes (HTTP 429). Agreed to include within API design. AP@Pedro to include in API Proposal + +### Next Steps + +- Next Meetings:
      +• 10th August - 13:00 - 14:00 CEST
      +• 31th August - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2ce94a3a8839436476b717a324b863cac12d2332 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10/raw.md @@ -0,0 +1,49 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 10-ago-2023
      +**Status:** FINAL + + + +## Attendees + +- Sebastian Köller (Vodafone) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
      +Open Issues
      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +Consent management in API | WG | Discussion about consent Management +Baseline API Proposal | TEF | Ongoing API v0.1 + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Sebastian (VF) and Georgios (DT) are fully operative. Klaus (VF) and Krzysztof (DT) are managing its access. PRs triggered to update [Maintaners](https://github.com/camaraproject/BlockchainPublicAddress/pull/14) and CodeOwners (pending) accordingly. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Telefonica provides more info about Use Cases. Vodafone comments the topic of how to manage the consent of accessing the information (GET List of Blockchains of a given phonenumber). If this endpoint can be accessed vía 2-legged how this access can be controlled in a way the user's phone owner can control the list of people they can view his blockchain addresses. Several initial options commented during the meeting (functionality to have whitelist option where indicate phonenumbers that can access blockchain of other phone numbers, hashing of blockchain and/or phone number). Need to have more discussion around the issue. New [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) created +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Proposal presented by Telefonica in order to address this comment. VF(Sebastian) seems OK to this proposal. Georgios (DT) would like to check offline, to identify whether can be 'scam' scenarios that may need currency. +Enhancement due to consent management | Explain the context of consent management within API. After meeting new [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) opened, summarizing info. Main topic concern raised here are (DT, VF) the following:
      • Whether this consent is "forever" or "one time use". Once User B gives consent, anyone could access to such info.
      • Whether this consent has to be more fine-grained, so as provided only for the User A access (i.e. have granularity to be settled per user phoneNumber level).

      TEF asks whether according to these comments it is being thinking in an UX where User B is prompted with a screen to give their consent for any API call for any User A's request, and response is yes. TEF will also check internally about its product view on that. Related to this, Rafał indicates that this has relationship with Identity&ConsentManagement WG and regarding picture provided just not to include (at least) within CAMARA API spec as it includes conventions outside CAMARA. It will be taken out and in future check if makes sense to add something GSMA OpenGateway agnostic. +AoB | Control of rate limit of requests, commented by Deustche Telekom. To have some rate control policy in Telco Operator API GW, needed to cover it in API design. Exception 429 already considered into the proposal. +Baseline API Proposal [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5)| Points performed:
      • Renamed OB to Telco Operator
      • Adding Exception 429
      • Removed Image.
      Pending Points:
      • `currency` topic
      • Impacts in API derived from Consent Management + + +### Next Steps + +- Next Meetings:
      +• 31th August - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4bdf613bee6e1635285b8a442660e6cdd54015f8 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31/raw.md @@ -0,0 +1,51 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 31-ago-2023
      +**Status:** FINAL + + + +## Attendees + +- Stefan Engelbert (Aloaha) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
      +Next Actions
      + + +Item | Who | Description +---- | ---- | ---- +MOM-2023-08-10 - [PR#17](https://github.com/camaraproject/BlockchainPublicAddress/pull/17) | WG | MOM-2023-08-10 +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +Baseline Proposal [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | TEF | Basline API Proposal +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management + + +### Items Discussion + +Item | Discussion +---- | ---- +Welcome to new members | Stefan Engelbert (Aloaha) joins the WG. +MOM-2023-08-10 - [PR#17](https://github.com/camaraproject/BlockchainPublicAddress/pull/17) | Pending Approval, reviewed by Georgios and Sebastian. Will ask Jose Antonio Lucena (TEF) in the meantime other codeowners are added to approve them, so it can be merged. CODEOWNERS and Maintainers files cannot be updated until involved people has WG access. Also Krzysztof will trigger PR to include as a codeowner so Pedro can approve it and therefore have codeowners in the short-term from two companies at least. +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | No news about Klaus status. Asked him offline. Check again next week. +Baseline Proposal [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Pedro comments TEF has intention to perform an MVP based on initial proposal and asks WG if we can merge it in order to be able to indicate CAMARA compliance. This does not enter in contradiction with the fact that API can and will be evolved based on output of discussions and future requirements. This version will be set as "v0.1". Also we will have a reference to evolve from it. It is understood within the WG and it is OK to move forward and merge. Pedro will check and make some refinements and advise for review. Intention is to merge (if possible) during 4th September week. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Georgios comments it will be needed more time to have a view about currency relationship with the Public Address. Then this issue will be KEPT OPEN. Also comments from Stefan, Krzysztof (topic of having some model to signal/identify chain_id), mentioning [https://chainagnostic.org/CAIPs/caip-2](https://chainagnostic.org/CAIPs/caip-2) (this reference was also provided during July) and Sebastian about potential anidated blockchain "type" model. Summary gathered within then issue and participants will comment over this. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro comments that this topic has raised internally but no feedback yet due to holidays period. In two directions:
      • About product perspective to manage consent in every GET access to the blockchain information of a given user
      • In the way of "having" API functionality to manage some kind of whitelists to "allow trusted contacts" the access without request consent. +AoB | Next Meetings, next meeting scheduled for 28th September. Pedro is on holidays next weeks and comments to the WG if any meeting would like to be managed in the meantime, 14th September could be an option (up to WG in case other members consider suitable) + +### Next Steps + +- Next Meetings:
      +• 28th September - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e6e89ac143b3e237484595f4448a226aeb910ef2 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28/raw.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-sep-2023
      +**Status:** FINAL + +## Attendees + +- Stefan Engelbert (Aloaha/CodeB) +- Rafał Artych (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Currently, initial baseline version (v0.1) is generated. A tag will be generated to track this baseline version (PR to be generated). Next steps are to progress in open issues and after that review Use Stories description. After meeting, Pedro (TEF) synchronized status with Krzysztof (DT) that joined later. Also bi-weekly meetings will be scheduled. +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Klaus (VF) and Krzysztof (DT) pending to enable their subscription to the WG. Sebastian (VF) will comment internally to Klaus and Pedro (TEF) comments offline to Krzysztof. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Pending comments by Georgios, issue is kept OPEN and to be reviewed in next meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro comments it will be reviewed internally with Product next week in order to have feedback. Initially, Use Case addressed by TEF is to set up consent once per user. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Sebastian (VF) explains rationale for this topic. Underlying idea is to have a (reduced) set of manually defined layer 1 blockchains and optionally use the chainId for layer 2 blockchains or testnets within that ecosystem. For instance for EVM-based chains, there is an already defined chainId for them in https://chainlist.org/. Stefan (CodeB) agrees with this proposal baseline. Pedro (TEF) will check in detail. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 5th October - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..05df8986d9fca473b9191960fe2053bae3093333 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05/raw.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 05-oct-2023
      +**Status:** FINAL + +## Attendees + +- Stefan Engelbert (Aloaha/CodeB) +- Rene Reinsberg (Celo Foundation) +- Kevin Tharayil (Celo Foundation) +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | New members from Celo Foundation joined the meeting (Rene, Kevin). They refer during the meeting to some initiatives they have been involved: [Minipay](https://www.opera.com/de/products/minipay) and [Valora](https://valoraapp.com/)

      With regards to WG status, next step is to generate a release for the initial version v0.1.0, [PR#23](https://github.com/camaraproject/BlockchainPublicAddress/pull/23) to generate `CHANGELOG.md` is ready and will be merged after meeting.
      Work done after the meeting.
      • New Release tag [v0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/v0.1.0) generated.
      • Release content [release-0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/tree/release-0.1.0) +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | To make more agile WG work, Georgios (DT) and Sebastian (VF) are settled as both maintainers [PR#14](https://github.com/camaraproject/BlockchainPublicAddress/pull/14) and codeowners [PR#24](https://github.com/camaraproject/BlockchainPublicAddress/pull/24). When Klaus (VF) and Krzysztof (DT) enable their subscription we will comment to include as maintainers and codeowners. Both PRs are `MERGED` and the Issue is `CLOSED`. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Agreed to be closed. `CLOSED` after the meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro (TEF) illustrates the topic for anyone to have some background and also indicates have internally address this with their product team and their concern is that the checking for the permission for every transaction may be a stopper for business cases as it is not the best performance, also indicates that probably some product guidance from GSMA OGW would be helpful. Sebastian indicates that it should be avoided that personal information can be leaked by anyone and we should ensure the restricted access to this information. Georgios also comments not only the access to blockchain info but the knowledge of phone numbers that can be used for spaming services. In this context, Celo comments about some work they have performed in [user identity in blockchain](https://docs.celo.org/protocol/identity/odis-use-case-phone-number-privacy). +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Rationale of the proposal explained by Sebastian is understood. Georgios comments the proposal is in line with the objective of a better blockchain identification scheme. Pedro also comments it is a good way forward and asks some clarification questions, about the identification of ethereum mainnet in this model (blockchain=evm, chainId=1) and to check this proposal does not enter in contradiction with the use of DID for the identification of the blockchain address, where Sebastian indicates there is no constrain/restriction. Pedro will draft a proposal within the issue to get a consensus on this. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 19th October - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f2abc43ac83ab78f105c7ebd0235e25c8e368a36 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19/raw.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 19-oct-2023
      +**Status:** FINAL + + +## Attendees + +- Kevin Tharayil (Celo Foundation) +- Rafał Artych (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +WG Kick-Off Meeting
      + + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Two topics commented:
      • WG repository information after release generation and merging of [PR#25](https://github.com/camaraproject/BlockchainPublicAddress/pull/25). New release is available [Release v0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/v0.1.0) and [CHANGELOG.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/CHANGELOG.md) and [README.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/README.md) are updated.
      • Manage members subscription: Klaus and Krzysztof will re-trigger the WG subscription request so as they will enable their subscription and link their github user. Later on, it will be possible to manage them as maintainers/codeowners. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Sebastian presented a proposal in order to manage every type of blockchain. Relying in one parameter to identify L1 Ecoystems and other one for identifying L2 and subsequent levels. Pedro and George seems initially OK. Latest comment of using `ethereum` instead of `evm` was in line to indicate real L1 ecosystems within 'blockchain' field, so the reason to also indicate other ecosystems like Avalanch even they have a chainId in evm naming format. This was explained in the meeting as asked by Krzysztof as a doubt. Krzysztof also mentioned whether the list of supported chainIds has to be restricted, Klaus comments that should be left open (initially no restriction in API input); Pedro indicates that in principle API design can support all and to deal with those business scenarios where a given chainId is not supported (a user wallt that does not manage specific blockchains) an exception may be defined. There is more discussion around this topic ( Krzysztof refers to CAIP - https://chainagnostic.org/CAIPs/caip-2, Klaus also mention to other scheme https://eips.ethereum.org/EIPS/eip-3220), in order to have a flexible way to identify a huge amount of blockchain ecosystems. There is certainty about evm chainId (https://chainid.network/, https://chainid.network/chains.json) is unique for evm based chains. After some discussion, Klaus comment the idea of having the identification in a common parameter (name to be decided, WG thinks offline) and that parameter indicates the L1-"sub-id" in a flexible way. It seems a way forward and WG will think about a name. In the meantime Pedro will trigger WIP PR to begin to detail this proposal and also improve/evolve with comments received. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF (Pedro) explains this topic can be resumed in order to improve/enhance description of Use Cases with the context discussed these months. Also provides information about Use Cases TEF business is thinking about. To be checked offline and provide feedback by WG members. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Not covered during this meeting. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 2nd November - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..dc16a9e75f5cbef0f27350330ee5a1efa00dcf9d --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02/raw.md @@ -0,0 +1,41 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 02-nov-2023
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +[PR#29](https://github.com/camaraproject/BlockchainPublicAddress/pull/29) | WG | Create MOM-2023-10-19 +[PR#31](https://github.com/camaraproject/BlockchainPublicAddress/pull/31) | DT | Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +Create MOM-2023-10-19 - [PR#29](https://github.com/camaraproject/BlockchainPublicAddress/pull/29) | Meeting Minutes of 19th October Meeting ready for review. Commented during the meeting the review of them to have the approval and merge them. +Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository - [PR#31](https://github.com/camaraproject/BlockchainPublicAddress/pull/31) | PR triggered by DT (Rafał) in order to align WG repository with the guidelines of CAMARA regarding [Testing Folder](https://github.com/camaraproject/Template_Lead_Repository/pull/1). Reviewed and approved. `MERGED` after the meeting +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | As commented during last meeting, Pedro triggered a PR to compile the output of the Issue. The proposal is under [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30), along with other Commonalities alignments and editorial enhancements. The target name of the parameter to identify the blockchain is still TBD (currently appears as `blockchain`). Pedro (TEF) indicates it is still pending to add the exception to manage the scenario mentioned by Krzysztof (DT) in the last meeting, but generated in advance to receive comments from the participants. Georgios (DT) gave an OK to the proposal in terms of the description provided. Krzysztof (DT) and Sebastian (VF) will review offline. Sebastian also asks two points:
      • If Issue#19 will be closed after the merging of this PR, and Pedro indicates that this is the objective (keeping v0.2.0-wip, just to discuss later within the WG the next steps).
      • The meaning of `` within the blockchain identification model, where Pedro answers it is the name given to the concept under L2 and Testnets blockchain identification (in EVM it matches the concept of chainId), and it is open to receive inputs if other name is considered more suitable, and for sure it can be reviewed in the future. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Commented during the meeting to check this issue by participants in order to receive comments and see if further description is incorporated into Use cases description document. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF indicates next week will synchronize this point internally with Business and comment back to the issue. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 16th November - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c1cb7b8d124824672b31fa0133da57919b8a3a82 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 16-nov-2023
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jorge Ordovas (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Today joins meeting Jorge Ordovas (TEF, Business Unit Web3 proyects). Currently main focus within WG is an aligment in Blockchain Identification Model. Meeting Minutes from [19/OCT](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/documentation/MeetingMinutes/MOM-2023-10-19.md) and [02/NOV](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/documentation/MeetingMinutes/MOM-2023-11-02.md) are available. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Proposal is under [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30), some wording comments provided by Rafał (DT), already fixed. Also he refers to Commonalities Issues [camaraproject/Commonalities#77](https://github.com/camaraproject/Commonalities/issues/77) and [camaraproject/Commonalities#80](https://github.com/camaraproject/Commonalities/issues/80), which are noted to be addressed in this PR or a future one, based on their respective output.
      Some background context is provided for Jorge (TEF) also understands the rationale of this track.
      Pending point is to agree on a field name for this concept, some suggestions provided by Pedro (TEF) within the Issue. Georgios (DT) indicates his preference is `blockchainNetworkId` and also asks whether makes sense to have some alignment in the wording for the BlockChainPublicAddress. Pedro (TEF) comments doesn't think so as this field is to indicate which Blockchain Network the BlockchainPublicAddress belongs to. Some days will be given to provide preferences among participants and selected name will be updated within PR, so as setting for final review. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Will be closed during this week if no further comment provided. It can be also discussed in the future. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Feedback from TEF. Business Unit is performing Privacy Assesment about this funcionality, therefore will be kept On-Hold until having their input about this. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 30th November - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3e47bf3c1286added0eed9268ec554b9fa4f4880 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 30-nov-2023
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | After [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) merge, v0.2.0-wip is available in code folder. So far, it will be kept `ON-HOLD`, until some Commonalities guidance are being resolved (i.e. AuthN/AuthZ section), so it can take advantage before generating a new release if required. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | `CLOSED` after review and approval of [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) by Georgios (DT) and Sebastian (VF) respectively. [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) is `MERGED` during the meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Feedback from Pedro (TEF). Business Unit Privacy Assesment is still pending and probably will happen next year. Will be kept `ON-HOLD` until it. +AoB | Some topics during the meeting:
      • Georgios (DT) asks whether implementation topics are discussed within CAMARA WG scope. Pedro (TEF) comments implementation is not under the scope of CAMARA but probably hosted in the context of Operators meetings within each country, where alignment about implementation of different APIs/features is taking place (a.k.a. local champions).
      • Pedro (TEF) indicates it will trigger a new PR to add Krzysztof as codeowner.
      • Sebastian (VF) shares with the WG he will be leaving it by the end of this year. WG appreciates the effort and contribution from Sebastian during these months. A PR will be triggered to removed him as a maintainer and codeowner.
      • Agreed to have next meeting on 12th December (same slot), being the latest during this year. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 12th December - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c1b771c69711d19d319fca4467c4ad1c423cedec --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12/raw.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 12-dec-2023
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Jorge Ordovas (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +Maintainers and Codeowners | WG | Update Maintainers and Codeowners +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | API specification v0.2.0-wip is available in code folder. Kept `ON-HOLD`, until some Commonalities guidance are being resolved (i.e. AuthN/AuthZ section), so it can take advantage before generating a new release if required. To be reviewed next year. +Maintainers and Codeowners | Update of maintainers and codeowners:
      • Maintainers - [PR#35](https://github.com/camaraproject/BlockchainPublicAddress/pull/35) `MERGED`: Removed Jose Antonio (TEF) and Sebastian (VF).
      • Codeowners - [PR#36](https://github.com/camaraproject/BlockchainPublicAddress/pull/36) `MERGED`: Removed Jose Antonio (TEF) and Sebastian (VF). Added Krzysztof (DT). +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Kept `ON-HOLD` until next year. +AoB | Some topics during the meeting:
      • Pedro (TEF) will ping offline Klaus (VF) to check whether is going to participate within the WG next year as Sebastian has leaved the WG.
      • Pedro (TEF) comments WG about existance of slack channel that may help to be more agile in tech discussions. [Link](https://join.slack.com/t/camara-project/shared_invite/zt-23bjzwes5-4aLBtE_E1sO0BJhCLBdZVQ).
      • Rafał (DT) comments about traversal work regarding CAMARA linting rules. Main contributions are [Commonalities/PR#74](https://github.com/camaraproject/Commonalities/pull/74) and [Commonalities/PR#110](https://github.com/camaraproject/Commonalities/pull/110). Ask for volunteers to apply in Blockchain (Pedro offers as volunteer, will open an issue to track it). Krzysztof (DT) asks about the WoW and Rafał comments the initial intention is to test these linting rules in every CAMARA WG to check its behaviour and make refinements if any. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 11th January - 13:00 - 14:00 CEST
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..263722d2799c62fba06d113156d3a54ba63e8050 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-jan-2024
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jorge Ordovás (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | WG | Linting rule set for Blockchain Public Address API +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | The meeting was a brief update on some administrative and technical topics of the blockchain working group. The main points discussed were:
      • Asked Georgios as codeowner to review and approve the minutes of the last meeting.
      • Pedro said that he will be contacting Klaus to know if he is planning to attend again the working group.
      • Pedro proposed to have meetings based on demand and to use the blockchain slack channel to communicate the topics of the next meetings. Georgios and Rafał agreed with Pedro's approach.
      • Pedro suggested to keep the current evolution of the justification until the discussions on the blockchain identification and the commonalities were resolved. +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Still `ON-HOLD` waiting for the business feedback on a privacy evaluation/assesment. +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | Pedro shared that he already applied the linter in a fork. Thanks to Rafał support and guidelines to enable this. A thread will be opened in the Issue#38 to comment on the results and the necessary particularizations for blockchain. Rafał added that the linter rules might need some changes or updates comming from Commonalities track. +AoB | Next pending points are:
      • Review the output of the linter and make the necessary adjustments in the API specification.
      • Follow the thread of the Issue#38 and provide comments or suggestions.
      • Consult with the business team if there was any new requirement or prioritization for the new year.
      • Be attentive to the business feedback on the issue #16 and decide how to proceed.
      • Join the slack channel of blockchain for participants and be aware of the calls for the next meetings. + + +### Next Steps +- Next Meetings:
      + • Next meeting: TBD, on demand
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f9b625769c174506a3e3f2e666ae87881ae2aede --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22/raw.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-feb-2024
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Jorge Ordovás (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | WG | Linting rule set for Blockchain Public Address API +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | **Linter Rules**: The linter rules from commonalities have been tested successfully and will be applied to the working group repository. New Issue and related PR will be triggered in the next weeks. AP@Pedro
      **New Topic**: An issue will be created to discuss how to handle the scenario of requesting a binding for a configuration that already exists. The proposed solution is to use the 409 conflict error code. AP@Pedro +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | The issue of consent management and privacy will be resumed in the next meeting, as there is no clear business feedback yet. Pedro wants to have some guidelines or conclusions to move forward with this topic. Agreed by Jorge, Georgios, Krzysztof, Rafał. +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | Linter tested OK, then issue is `CLOSED`. +AoB | Pedro contacted Klaus (VF) offline and informed that Klaus will not join the working group for the time being (short-term). Maybe in the mid-term. He will follow offline the progress.
      Next meetings (next two months due to Pedro personal matter) will be moved temporarily to 11:00 - 12:00 CET Time. Agreed by the team. NOTE: Changed after the meeting to 11:30 - 12:30 for Jorge to be able to attend.

      Pending points for the next meeting are:
      • Discuss the issue of consent management and privacy and try to reach a conclusion or a way-forward.
      • Review the issue and the pull request for the 409 conflict error code scenario. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 7th March, 11:30 - 12:30 CET
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c725246d5454f8622637acde5de0c2c6adb95826 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07/raw.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-mar-2024
      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#46](https://github.com/camaraproject/BlockchainPublicAddress/issues/46) | TEF | Manage Duplicated Bindings and Improve Description +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | **Linter Rules**: Linter rules applied and working successfully. Thanks to all support from Rafał.
      **Meeting Minutes 22th/February**: [Minutes](https://github.com/camaraproject/BlockchainPublicAddress/pull/43) approved and `MERGED`. +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Georgios, Rafal and Jorge cannot attend the meeting. The issue is postponed until the next meeting. +[Issue#46](https://github.com/camaraproject/BlockchainPublicAddress/issues/46) | Manage Duplicated Bindings and Improve Description. Issue opened by Telefonica, to address the case when a binding with a specific configuration (phoneNumber, blockchainNetworkId, blockchainPublicAddress and optionally currency) already exists, and a new one (POST) with the same configuration is triggered. The proposed exception is `HTTP 409 - CONFLICT`. Also some description rewording and fixing is proposed. Commented during the meeting to be reviewed offline and talk in the next meeting. Generated related [PR#47](https://github.com/camaraproject/BlockchainPublicAddress/pull/47). +AoB | Pedro indicates he is not able to attend next meeting (21th March). Rafał also cannot. Then the next meeting will be held on 4th April. + + +### Next Steps +- Next Meetings:
      + • Next meeting: 4th April, 11:30 - 12:30 CET
      diff --git a/marked/BlockchainPublicAddress/documentation/MeetingMinutes/README/raw.md b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..72fe52867bd27e3e0e8eecdc9d2181bb9ad0bb15 --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since 4th April WG Meeting, meeting minutes are placed in [CAMARA Blockchain Public Address WG Wiki Confluence site](https://lf-camaraproject.atlassian.net/wiki/x/thDe) \ No newline at end of file diff --git a/marked/BlockchainPublicAddress/documentation/SupportingDocuments/README/raw.md b/marked/BlockchainPublicAddress/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/BlockchainPublicAddress/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/CallForwardingSignal/README/raw.md b/marked/CallForwardingSignal/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..58f6eb0ca1ab3c6d1e7fa6a2650b799701b1b862 --- /dev/null +++ b/marked/CallForwardingSignal/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# CallForwardingSignal + +Incubating API Repository to evolve and maintain the definitions and documentation of CallForwardingSignal Service API within the Sub Project [Call Forwarding Signal](https://lf-camaraproject.atlassian.net/wiki/x/IIAfBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/HADe) + +## Scope +* Service APIs for “CallForwardingSignal” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * retrieve information about the status of the Call Forwarding Service on a specific phone number. + * avoid fraud leveraging the Call Forwarding Service. + * The main scope of the Call Forwarding Signal API is anti fraud to avoid fraudsters to use the Call Forwarding Service to carry on a scam. Other use cases are anyway supported by the Call Forwarding Signal API that also provides additional endpoints to detect the general Call Forwarding Service settings. +* Describe, develop, document and test the API +* Started: February 2024 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.3](https://github.com/camaraproject/CallForwardingSignal/releases/tag/r3.3) (Fall25), with the following API versions: + * **call-forwarding-signal v0.4.0** + [[YAML]](https://github.com/camaraproject/CallForwardingSignal/blob/r3.3/code/API_definitions/call-forwarding-signal.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CallForwardingSignal/r3.3/code/API_definitions/call-forwarding-signal.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CallForwardingSignal/r3.3/code/API_definitions/call-forwarding-signal.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CallForwardingSignal/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CallForwardingSignal/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CallForwardingSignal/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Monday 15h-16 CET, usually every two weeks. For the next meetings information, have a look on the [API Wiki Page](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14549020/CallForwardingSignal). + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96706226837?password=2d113354-bf97-4441-8d6d-9fd0ae69f2d1) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14574452/CallForwardingSignal+Minutes?atlOrigin=eyJpIjoiNjc1Mzc3ZWIwNGI4NGRhMmE2YjBkMGFjNmFjMTNiZDUiLCJwIjoiYyJ9) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to all Contributors of this Sub Project can be sent using . diff --git a/marked/CallForwardingSignal/code/API_definitions/call-forwarding-signal/raw.md b/marked/CallForwardingSignal/code/API_definitions/call-forwarding-signal/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2bac19c900e02ce563b87e64f8bbef8033989ee9 --- /dev/null +++ b/marked/CallForwardingSignal/code/API_definitions/call-forwarding-signal/raw.md @@ -0,0 +1,603 @@ +# call-forwarding-signal + +```yaml +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Call Forwarding Signal + description: | + # Overview + The Call Forwarding Signal API provides the API Consumer with + information about the status of the Call Forwarding Service on a specific + phone number. The main scope of the Call Forwarding Signal API is "anti + Fraud" to avoid fraudsters to use the Call Forwarding Service to carry + on a scam. Other use cases are anyway supported by the Call Forwarding + Signal API that also + provides additional endpoints to detect the general Call Forwarding + Service settings. + # Introduction + The Call Forwarding Service is provided by the Network to a phone + number. This service redirects the incoming call to that phone number + to an alternative destination such as another phone number or a voice mail + system. There are two main types of call forwarding settings: + unconditional and conditional. + The Call Forwarding Signal API can be invoked to detect if the unconditional + call forwarding service is active. The Call Forwarding Signal API can also + be invoked to + get the general status of the Call Forwarding Service (inactive, + conditional, unconditional). If conditional call forwarding is active, + the different type of settings are returned ('conditional_busy', + 'conditional_not_reachable', 'conditional_no_answer'). + + **Example use cases:** + + [**Bank Frauds**](https://github.com/camaraproject/CallForwardingSignal/discussions/3#discussioncomment-8694420) + + [**Alert Interception**](https://github.com/camaraproject/CallForwardingSignal/discussions/3#discussioncomment-8701847) + + [**Call Forwarding Verification**](https://github.com/camaraproject/CallForwarding\Signal/discussions/3#discussioncomment-8915595) + # Quick Start + The Call Forwarding Signal API is a REST API based on the + CreateCallForwardingSignal resource. + This resource can be used, by the API Consumer, to specify the phone number + on which the Call Forwarding Service status must be verified, in case of + two-legged authentication. If three-legged authentication is used the phone + number is instead detected, by the API Producer, from the access token. + + Before starting to use the Call Forwarding API, the developer needs to know + about the below specified details: + + **phoneNumber** + This is the end user phone number. The Call Forwarding Signal API verifies + if a call forwarding + service is active on this phone number. Note: this parameter must be + must be provided/valued only in case of two-legged authentication. + In case of three-legged authentication the phone number is retrieved by + the access token. + + **CreateCallForwardingSignal** + This is the resource the API Consumer uses to define the phone number to + be verified about the status of the Network Call Forwarding service. + + **UnconditionalCallForwardingSignal** + This is the resource the API Consumer gets back, containing the information + about the Unconditional Call Forwarding Service status for the given phone + number (PhoneNumber). + + **CallForwardingSignal** + This is the resource the API Consumer gets back, containing the information + about the general status of the Network Call Forwarding service for the + specified phone number. + + The Call Forwarding Signal API provides two endpoints fulfilling the + following intents: + - **unconditional-call-forwardings**: Is the unconditional call fwd service + active on a specific phone number? + - **call-forwardings**: Which is the status of the call forwarding for a + specific phone number? + # API Documentation + ## Details + The Call Forwarding Signal API is invoked by an API Consumer after the + Consent Management flow. + + The API Consumer can request the API Producer for the status of the + Unconditional Call Forwarding service using the + unconditional-call-forwardings POST method. A boolean, with the information + about the activation status of the call forwarding service, will be + provided back via the UnconditionalCallForwardingSignal resource. + + The API Consumer can also request the API Producer for the generic status of + the Call Forwarding service using the call-forwardings POST method. An array + of strings with the information of the type of active call forwarding + services will be provided back via the CallForwardingSignal resource. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Identifying the phone number from the access token + This API requires the API consumer to identify a phone number as the + subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject + will be identified from the optional `phoneNumber` object field, which + therefore MUST be provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a + three-legged access token to invoke the API by relying on the + information that is associated with the access token and was + identified during the authentication process. + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `phoneNumber` object field is not included in the request, then + the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the + optional `phoneNumber` object field is also included in the request, then + the server will return an error with the `422 UNNECESSARY_IDENTIFIER` + error code. This will be the case even if the same device is + identified by these two methods, as the server is unable to make + this comparison. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + # FAQ's + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/CallForwardingSignal +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/call-forwarding-signal/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +############################################################################ +# Tags # +############################################################################ +tags: + - name: Unconditional Call Forwarding information retrieval + description: Provides information on Unconditional Call Forwarding + settings for the provided phone number (PhoneNumber) + - name: Call Forwarding information retrieval + description: Provides information on Call Forwarding settings for the + provided phone number (PhoneNumber). +############################################################################ +# Paths # +############################################################################ +paths: + /unconditional-call-forwardings: + post: + tags: + - Unconditional Call Forwarding information retrieval + security: + - openId: + - 'call-forwarding-signal:unconditional-call-forwardings:read' + summary: Retrieve the information about the status of the + unconditional call forwarding service on a phone number (PhoneNumber) + description: This endpoint provides information about the status + of the unconditional call forwarding, being active or not. + operationId: retrieveUnconditionalCallForwarding + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallForwardingSignal' + required: true + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/UnconditionalCallForwardingSignal' + "400": + $ref: "#/components/responses/Generic400" + '404': + $ref: '#/components/responses/Generic404' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /call-forwardings: + post: + tags: + - Call Forwarding information retrieval + security: + - openId: + - 'call-forwarding-signal:call-forwardings:read' + summary: Retrieve the information about the type of call forwarding + service active on a phone number (PhoneNumber) + description: This endpoint provides information about which type of + call forwarding service is active. More than one service can be + active, e.g. conditional and unconditional. This endpoint exceeds + the main scope of the Call Forwarding Signal API, for this reason + an error code 501 can be returned. + operationId: retrieveCallForwarding + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallForwardingSignal' + required: true + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/CallForwardingSignal' + "400": + $ref: "#/components/responses/Generic400" + '404': + $ref: '#/components/responses/Generic404' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "501": + $ref: "#/components/responses/Generic501" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + description: to support Consent Management + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ############################################################################ + # Resources # + ############################################################################ + schemas: + UnconditionalCallForwardingSignal: + description: resource containing the information about the Unconditional + Call Forwarding Service for the given phone number (PhoneNumber) + type: object + properties: + active: + type: boolean + description: Indicates if the unconditional call forwarding service + is active. + CallForwardingSignal: + description: resource containing the list of the Call + Forwarding Services active for the given phone number (PhoneNumber). The + possible states are, 'inactive' (no call forwarding service activated), + 'unconditional' (call forwarded independently from the device status), + 'conditional_busy' (call forwarded if the device is on an active call), + 'conditional_not_reachable' (call forwarded if the device is not + reachable), 'conditional_no_answer' (call forwarded if the device doesn't + answer the incoming call). + type: array + items: + type: string + enum: + - 'inactive' + - 'unconditional' + - 'conditional_busy' + - 'conditional_not_reachable' + - 'conditional_no_answer' + example: + - 'unconditional' + - 'conditional_busy' + - 'conditional_no_answer' + minItems: 1 + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Request # + ############################################################################ + CreateCallForwardingSignal: + description: resource containing the phone number (PhoneNumber) regarding + which the Call Forwarding Service must be checked. To be provided/valued + only in case of two-legged authentication. If provided/valued with + three-legged authentication a 422-UNNECESSARY_IDENTIFIER error code is + returned. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + ############################################################################ + # Types # + ############################################################################ + PhoneNumber: + description: A public identifier addressing a telephone subscription. + In mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to E.164 + standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + ############################################################################ + # Responces # + ############################################################################ + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Call forwarding check can't be done because the + phone number is unknown. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the + request and the device or phone number identification + cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when + a device or phone number has already been identified + from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the + access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code + should be avoided as far as possible to get the objective + to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. +``` diff --git a/marked/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1/raw.md b/marked/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ae4d5d68c12825f46ca29d83409f8f6603435183 --- /dev/null +++ b/marked/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1/raw.md @@ -0,0 +1,15 @@ + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Banks offer the option for end users to receive telephone calls to solve problems, e.g. in case of issues with the bank App, issues with Smartphones, the bank website or any tool providing access to the online bank account management system. How does the fraudster operate?
      • Through social engineering, the fraudster gathers information about bank end users who are engaged in such a situation, needing the bank to contact them.
      • Once they identify the service provider and the phone number of an end user, they manage to successfully activate, on the end user's profile, the 'unconditional call forwarding' to a phone number they control.
      • After successfully setting up 'unconditional call forwarding,' the fraudster then contacts the bank, claiming an inability to access online banking services and requesting a call from a bank representative.
      • When the bank calls the registered contact number of the end user, the active 'unconditional call forwarding' diverts the call directly to the fraudster, thus completing their scheme.
      The Bank Application, before contacting the end user's phone number, invokes the Call Forwarding Signal API to verify if a "unconditional call forwarding" option is active on the end user's phone, avoiding such a fraud| M | +|Roles, Actor(s) and scope|Bank Application: role of Call Forwarding Signal API consumer
      API Provider: role of Call Forwarding Signal API provider
      End User: role of owner of the phone number to be verified
      Scope: Anti fraud| M | +|NF Requirements|| O | +|Pre-conditions|• The Bank Application is aware of the End User's phone number
      • The End User gave the consent to check for the Call Forwarding Service activation on his phone number.| M | +|Begins when|The Bank Application invokes the Call Forwarding Signal API to get the information on the status of the Unconditional Call Forwarding Service for his End User's phone number.| M | +|Step 1|The API Provider identifies the Bank Application as a valid Call Forwarding Signal API Consumer| M | +|Step 2|The API Provider verifies the User Consent| M| +|Step 3|The Bank Application invokes the Call Forwarding Signal API Producer providing the End User's phone number asking for the status of the Unconditional Call Forwarding Service | M | +|Step 4|The Call Forwarding Signal API Producer checks if the End User's phone number has an active Unconditional Call Forwarding Service| M | +|Ends when|The Call Forwarding Signal API Producer notifies the Bank Application about the status of the Unconditional Call Forwarding Service| M | +|Post-conditions|The Bank Application is aware of the status for the Unconditional Call Forwarding Service for the End User's phone number | M | +|Exceptions|Step 4 can generate an exception to be notified to the Bank Application| M | diff --git a/marked/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist/raw.md b/marked/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e1f66c98686fc2f1737d42af17e777cf59b86e52 --- /dev/null +++ b/marked/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ + +# API Readiness Checklist + +Checklist for API call-forwarding-signal v0.4.0 in r3.3 + + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/call-forwarding-signal.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.4.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/CFS_UserStory_UseCase-1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [call-forwarding-signal-every-forwarding](/code/Test_definitions/call-forwarding-signal-every-forwarding.feature), [call-forwarding-signal-unconditional](/code/Test_definitions/call-forwarding-signal-unconditional.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [call-forwarding-signal-every-forwarding](/code/Test_definitions/call-forwarding-signal-every-forwarding.feature), [call-forwarding-signal-unconditional](/code/Test_definitions/call-forwarding-signal-unconditional.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/uoDVB) | + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/marked/CallForwardingSignal/documentation/MeetingMinutes/README/raw.md b/marked/CallForwardingSignal/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fbbafcf24a831aca910f496d8bde289dae7555d8 --- /dev/null +++ b/marked/CallForwardingSignal/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,5 @@ +## Meeting Minutes of Call Forwarding Signal Sub Project + +Starting with the beginning of 2024 the meeting minutes of Call Forwarding Signal calls are within the CAMARA Wiki at: + +https://wiki.camaraproject.org/display/CAM/SP-CFS+Minutes diff --git a/marked/CallForwardingSignal/documentation/SupportingDocuments/README/raw.md b/marked/CallForwardingSignal/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/CallForwardingSignal/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/CapabilitiesAndRuntimeRestrictions/README/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c6a3aef678c1ccc7d91b11c046713992a735031c --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/README/raw.md @@ -0,0 +1,43 @@ + + + + + + + + + +# CapabilitiesAndRuntimeRestrictions + +Sandbox API Repository to describe, develop, document, and test the CapabilitiesAndRuntimeRestrictions Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/6YAjAw) + +## Scope + +* Service APIs for “CapabilitiesAndRuntimeRestrictions” (see APIBacklog.md) +* The CAMARA Runtime Restrictions API allows API consumers to understand and adapt to environment-specific differences in how CAMARA APIs are implemented. It provides details on what is supported, what is temporarily unavailable, and any other limitations that might affect how you call and consume those APIs. This API provides that information about other CAMARA APIs. +* The API provides the API consumer with the ability to: + * Discover Capabilities and Constraints + * Stay updated on changes + * Adapt your requests Automatically +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Tuesdays 1400-1500 UTC, every two weeks. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96678356438?password=706020d3-07bc-4d90-a0d5-1d6b94452a53) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/6YAjAw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . + diff --git a/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ea6db26e94f9ebb4b62c107d8ba8314866a9dd12 --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi/raw.md @@ -0,0 +1,1377 @@ +# camara-service-capability-openapi + +```yaml +--- +openapi: 3.0.3 +info: + title: CAMARA Service Capability API + description: | + The CAMARA Service Capability API provides programmable interface for developers and other users (capabilities consumers) to discover and be notified + about active/inactive capabilities (functions) for APIs. + + It delivers a tailored service capability based on consumer context, supporting complex request bodies, endpoint removal, and dynamic restrictions. + + # Introduction + This API enables feature discovery and near-real-time feature status notifications for APIs provided by the gateway / provider. + + Overlay-based restrictions use JSON Schema Validation (draft-bhutton-json-schema-validation-01) keywords and ensure restriction-only constraints. + The specification supports dynamic tailoring via `POST /camara/service/capability/v0`, which returns a restriction mapping with bit positions, capability identifiers, + and a mapping version. Initial restriction states are included in the successful response. Restriction state changes are notified via CloudEvents using bitmap-only + payloads for restrictions and leveraging the restriction mapping for synchronization. Versioning ensures consumers adapt to mapping changes. + + Overlays conform to the OpenAPI Overlay specification (https://spec.openapis.org/overlay/latest.html) and are evaluated at run-time rather than build-time on API consumer side using + context-aware logic. Only schema-restrictive updates are allowed (e.g., narrowing enums, removing operations). These extensions enable fine-grained control over API capabilities + by applying restriction-only constraints to schemas, body fields, and headers/parameters, respectively. + + An **API** (Application Programming Interface) often includes **features** that can be *active* or *inactive* during + interactions with API consumers. For example, feature negotiation during session establishment or events such as high congestion that + change a feature's status. + + **Capabilities** represent a collection of features and their **status** (*active* or *inactive*) at runtime. + These capabilities provide a way to describe what an API can do. + + **Footprints** define the coverage area where specific capabilities are available. A device must be located within the footprint to access + these capabilities. If no footprint is specified, the capabilities *may* be available to *any* device connected to the network. Footprints + have a *usage type* that determines their visibility and use. For example, some footprints may only be visible to Access Networks where + devices are attached, while others may be visible to Internet servers or services in a Non-Access network. Some footprints + may even be used in both types of networks. + + The API provider MAY have full knowledge of whereabout of the device, thus directly notifying the capabilities consumers + with near-real-time capability changes resulting of device location change without using footprints. This would reduce the additional footprint processing requirement at the consumer side + when the device receives the capability notification and capability info. + + When footprints are used, they are presented as part of a collection. A device is considered to be covered by a footprint collection if it + falls within at least one footprint in the collection. Footprint *precedence* specifies the search execution order of footprints in the + collection. The lower the numerical value of precedence, the higher the footprint precedence. Footprints with equal precedence MAY be + executed in parallel if supported by the system. (see *Usage* for more detail). + + To convey the impact of capability status to API consumers in a meaningful way, capabilities are directly tied to a set of **Runtime Restrictions**. + These restrictions affect optional or alternative structures, parameters, and other aspects of API usage. + + # Usage + The Camara Service Capability API enables clients to discover and manage CAMARA API capabilities + through a simple, RESTful interface and receive automatic CloudEvents when state changes. + ```mermaid + Client Webhook/Sink Capability API CloudEvents Broker + | | | | + |---------------------------------------->| | + | POST /camara/service/capability/v0 | | + |<----------------------------------------| | + | 201 + CapabilityInfo | | + | | | | + | | |----------------------> | + | | | Create Subscription | + | | | for capability | + | | | changes | + | | |----------------------->| + | | | Capability Changed | + | |<-------------------------------------------| + | | POST CloudEvent to Webhook | + | | | | + | |------------------------------------------->| + | | 204 | + | | | | + The Capability API responds with the supported capabilities and then internally + registers for capability change events if 'subscriptionRequest' is provided in the request. + As capabilities change event notifications are forwarded through a CloudEvents Broker to + the client-provided Webhook (Sink). + ``` + **How it works** + 1. **Query capabilities** + Client sends one or more `CamaraCapabilityQuery` objects to `/camara/service/capability/v0`. + 2. **Inspect response** + API returns a `CapabilityInfo` object with per-capability details, overlays, and restriction sets. + 3. **Receive updates automatically** + Whenever capability bitmaps or info change, the API emits a CloudEvent (via implicit subscription) + to your configured webhook sink endpoint. + **Supported CloudEvent types:** + - `org.camaraproject.capability.v0.capability-bitmap-changed` + - `org.camaraproject.capability.v0.capability-info-changed` + For full schema definitions and examples, see the components section below. + + ### Summary: + 1. `POST /camara/service/capability/v0`: Returns tailored CapabilityBitmap that assigns bit positions of each restriction, a mappingVersion for versioning for new restrictions. + 2. CloudEvents Notifications: Signals restriction state changes (active/inactive) via bitmap change event and new restrictions via info change event, ensuring efficient synchronization. + 3. Versioning: Uses mappingVersion to handle changes in the restriction mapping, preventing synchronization errors. + + # Relevant terms and definitions + * **Authentication**: + Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the Capability API. + * **API (Application Programming Interface)**: + A set of protocols and tools for building software and applications. + * **Features**: + Specific functions or capabilities of an API that can be *active* or *inactive*. + * **Capabilities**: + A collection of features and their status (*active* or *inactive*) at a specific point in time. + * **Footprints**: + Define the coverage area where specific capabilities are available. + * **Runtime Restrictions**: + Restrictions that affect optional or alternative structures, parameters, and other aspects of API usage using a collection of overlays. + There are two kinds of overlays. The openAPI Overlays specification is at https://spec.openapis.org/overlay/latest.html. + One kind is the static version of overlays which can be applied to the API spec at the build time of the + Client. The actions of the overlays are known to the Client before any runtime. Second kind is the one we're specifying in this CAMARA + Service Capability API specification where the overlays take effect at the runtime of the Client if the Client supports this specification. + The actions of any overlays are not known to the Client until they're communicated from the API provider at the runtime of the Client. + + # API functionality + Please see examples within this yaml on what options the gateway may return in the response. + + # Further info and support + + ## Frequently Asked Questions (FAQs) + 1. What is the purpose of the API described in the text? + The API enables feature discovery and near-real-time feature status notifications + for APIs provided by the gateway. + 2. What are capabilities and how do they relate to API features? + Capabilities represent a collection of features and their + status (*active* or *inactive*) at a specific point in time. These capabilities provide a way to describe what an API can do. + 3. What are footprints and how do they affect the availability of capabilities? + Footprints define the coverage area where specific + capabilities are available. A device must be located within the footprint to access these capabilities. If no footprint is specified, + the capabilities may be available to any device connected to the network. + 4. What is the role of footprint precedence in the search execution order? + Footprint precedence specifies the search execution order of + Footprints in the collection. The lower the numerical value of precedence, the higher the Footprint precedence. Footprints with equal + precedence may be executed in parallel if supported by the system. + 5. How do runtime restrictions affect API usage? + To convey the impact of capability status to API consumers in a meaningful way, + capabilities are directly tied to a set of runtime restrictions. These restrictions affect optional or alternative structures, + parameters, and other aspects of API usage using a collection of overlays. + 6. What if a Client does not support this API? + They can send requests without using this API. The downside + is that they may send requests that are invalid and could have been avoided with information from this API. They + could be more proactive by disabling / hiding options that are not enabled in the Client which improves user + experience. + 7. What if a Client does not support Footprints or a specific Footprint type? + They should ignore enforcing the + state of the specific capability. This may result in sending invalid requests. + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +servers: + - url: '{apiRoot}/camara-service-capability-openapi/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: CAMARA Service Capability Query + description: Returns the Service Capability for specified CAMARA service APIs + on the API gateway / producer side. + - name: CAMARA Service Capability notifications callback + description: Callback endpoint for receiving notifications on capability changes. +paths: + /camara/service/capability/v0: + post: + tags: [CAMARA Service Capability Query] + summary: Retrieve tailored service capabilities based on consumer context + description: | + Returns service capability information tailored to the consumer's context, including active/inactive restrictions and mapping metadata. + Successful response is with sets of restrictions based on consumer context, along with a restriction mapping assigning bit positions, + capability identifiers, and a mapping version. It includes response with initial bitmaps which should be enforced on the API consumer side. + operationId: postServiceCapability + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/If-None-Match' + - $ref: '#/components/parameters/If-Modified-Since' + security: + - openId: [camara-capability:read] + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CamaraCapabilityQueryRequest' + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE: + $ref: '#/components/examples/CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE' + callbacks: + notifications: + '{$request.body#/subscriptionRequest/sink}': + post: + tags: [CAMARA Service Capability notifications callback] + summary: CAMARA Service Capability notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any CAMARA Service Capability change related event occurs. + Currently only EVENT_CAPABILITY_CHANGED and EVENT_CAPABILITY_REMOVED events are defined. + operationId: postCapabilityNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents-batch+json: + schema: + type: array + items: + $ref: '#/components/schemas/CloudEvent' + examples: + EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE: + $ref: '#/components/examples/EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE' + EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE: + $ref: '#/components/examples/EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE' + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + security: + - notificationsBearerAuth: [] + responses: + '201': + description: Tailored Capability info with current restriction mapping + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + ETag: + $ref: '#/components/headers/ETag' + Cache-Control: + $ref: '#/components/headers/Cache-Control' + Last-Modified: + $ref: '#/components/headers/Last-Modified' + content: + application/json: + schema: + $ref: '#/components/schemas/CapabilityInfo' + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE: + $ref: '#/components/examples/CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE' + '304': + $ref: '#/components/responses/CapabilityNotModified304' + '400': + $ref: '#/components/responses/CapabilityApiBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/CapabilityApiNotFound404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + $ref: ../common/CAMARA_common.yaml#/components/securitySchemes/openId + notificationsBearerAuth: + $ref: ../common/CAMARA_common.yaml#/components/securitySchemes/notificationsBearerAuth + parameters: + x-correlator: + $ref: ../common/CAMARA_common.yaml#/components/parameters/x-correlator + If-None-Match: + $ref: ../common/CAMARA_common.yaml#/components/parameters/If-None-Match + If-Modified-Since: + $ref: ../common/CAMARA_common.yaml#/components/parameters/If-Modified-Since + headers: + x-correlator: + $ref: ../common/CAMARA_common.yaml#/components/headers/x-correlator + Cache-Control: + $ref: ../common/CAMARA_common.yaml#/components/headers/Cache-Control + ETag: + $ref: ../common/CAMARA_common.yaml#/components/headers/ETag + Last-Modified: + $ref: ../common/CAMARA_common.yaml#/components/headers/Last-Modified + schemas: + # General items used throughout the specification + Contexts: + description: | + An extensible container for reusable objects referenced by Overlays. It may reflect state of the API Service, client state, etc. + type: object + properties: + url: + type: string + format: uri + description: The resolved request URL. + method: + type: string + description: HTTP method in upper-case. + request: + $ref: '#/components/schemas/HttpMessage' + additionalProperties: true + required: [url, method, request] + HttpMessage: + type: object + description: Common structure for $request and, if supported, $response. + properties: + header: + type: object + # Valid header *names* (field-name = token) + description: | + A map of HTTP header fields. + **Header names (object keys)** SHOULD conform to the RFC-7230 `token` syntax: + `^[!#$%&'*+\-\.^_`|~0-9A-Za-z]+$` + Note: OpenAPI 3.0.3 cannot enforce key-name patterns natively. + additionalProperties: + type: string + pattern: ^[\t\x20-\x7E\x80-\xFF]*$ + description: Value of the header field (matches `field-value` ABNF) + query: + type: object + description: Query-string parameters; keys are already decoded. + additionalProperties: true + path: + type: object + description: Captured path parameters. + additionalProperties: true + body: + description: Request or response payload. Its shape depends on Content-Type. + additionalProperties: false + VersionedName: + description: | + An abstract base object containing names with versioning + type: object + properties: + name: + description: The item's name. Ideally, it is a unique value for its type. + This value MUST NOT contain the semicolon - ';' + type: string + example: cap1 + minLength: 3 + maxLength: 256 + pattern: ^[^;]*$ + version: + description: | + The semantic version of the object instance following [SemVer 2.0.0](https://semver.org/). + Examples: + - `1.0.0` + - `2.3.1-beta` + - `1.4.5+build.2025` + type: string + example: 1.0.0 + minLength: 1 + pattern: ^(0|[1-9]\d*)\.(0|[1-9]\d*)\.(0|[1-9]\d*)(?:-((?:0|[1-9]\d*|\d*[A-Za-z-][0-9A-Za-z-]*)(?:\.(?:0|[1-9]\d*|\d*[A-Za-z-][0-9A-Za-z-]*))*))?(?:\+([0-9A-Za-z-]+(?:\.[0-9A-Za-z-]+)*))?$ + specifyingBody: + description: Entity's specification organization (reversed fqdn format) + type: string + minLength: 1 + required: [name, version] + Footprint: + description: | + The coverage area to which capabilities apply. They help define the context in which the features are relevant. + There are many ways to describe a footprint -- for example, by address range (e.g., IPv4 CIDR or IPv6 CIDR (Classless Inter-Domain Routing), + network ID (e.g., Autonomous System Number (ASN)), nation boundaries (e.g., country code) or GPS coordinates. + When a **Footprint** value is not present, the capabilities apply to *any* connected device. + allOf: + - $ref: '#/components/schemas/VersionedName' + - type: object + properties: + footprintType: + description: | + Types include: + * [Content Delivery Network Interconnection](https://www.iana.org/assignments/cdni-parameters/cdni-parameters.xhtml#metadata-footprint-types) types + * [Geo position](https://www.iana.org/assignments/method-tokens/method-tokens.xhtml) types + * [Civic Address](https://datamodel.tmforum.org/en/latest/Common/Address/) types + * [Geographic Address type](https://github.com/tmforum-apis/TMF673_GeographicAddress) types + * [Geographic Location type](https://github.com/tmforum-apis/TMF675_GeographicLocation) types + * [Geographic Site type](https://github.com/tmforum-apis/TMF674_GeographicSite) types + * [ITU E.212 Mobile Country Code and Mobile Network Code](https://en.wikipedia.org/wiki/Mobile_country_code) values + * [GeoJSON](https://github.com/geojson/schema) + * [TopoJSON](https://github.com/topojson/topojson) + * [IP Geolocation Feeds (geofeed)](https://datatracker.ietf.org/doc/rfc8805/) + type: string + enum: + - ipv4cidr + - ipv6cidr + - asn + - countrycode + - altopid + - subdivisioncode + - footprintunion + - civicaddress + - geoposition + - itue212countrynetworkcode + - postaladdress + - geographicaddress + - geographiclocation + - geographicsite + - geojson + - topojson + - geofeedRFC8805 + footprintValue: + description: A list of footprint values. + type: array + items: + oneOf: + - type: string + - type: object + footprintUsage: + description: Indicates that the footprint value represents an Access + Network, a non Access Network, i.e., networks facing the Internet, + or both. + type: string + enum: [access, non_access, both] + precedence: + description: | + Specifies the search execution order of Footprints when they are part of a collection. The lower the numerical value of precedence, + the higher the rule precedence. Rules with equal precedence MAY be executed in parallel if supported. + type: integer + minimum: 0 + required: + - name + - version + - footprintType + - footprintValue + - footprintUsage + - precedence + Metadata: + description: > + Tighten validation, avoid client/server drift, and make structures robust. + type: object + properties: + description: + type: string + description: Human-readable description of the entity + createdAt: + type: string + format: date-time + description: | + RFC 3339 timestamp when this mapping was first published. + Providers must not set times in the future. + example: '2025-05-09T14:25:38Z' + lastModifiedAt: + type: string + format: date-time + description: | + RFC 3339 timestamp of the last non-breaking update. + Providers must not set times in the future. + example: '2025-05-10T12:03:00Z' + deprecatedAt: + type: string + format: date-time + description: RFC 3339 timestamp after which this entity is no longer be + applicable. + mappingHash: + type: string + pattern: ^[A-Fa-f0-9]{64}$ # SHA-256 in hex + description: SHA-256 digest of the canonical JSON representation of this + mapping. + example: 5d41402abc4b2a76b9719d911017c592cf0c58f2b3b65af6f88ab3a2b4d6996f + traceID: + type: string + description: Trace Identifier used across multiple systems. + + # Overlay imports + Overlay: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Overlay + Action: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Action-Object + Extends: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Extends + + # Camara extensions to Open API Overlay components + CamaraOverlay: + description: | + Common attributes of a CAMARA Overlay. + It extends OpenAPI Overlay Specification v1.0.0 for restriction-only schema patches. + allOf: + - $ref: '#/components/schemas/Overlay' + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + - type: object + properties: + actions: + description: A ordered list of actions + type: array + minItems: 1 + maxItems: 20 # DoS - guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CamaraAction' + operator: + description: | + Logical operator combining the results of all actions: + - **and**: all actions must succeed; processing stops on first failure + - **or**: failed actions are skipped + type: string + enum: [and, or] + default: and + required: [name, version, actions] + CamaraAction: + type: object + description: | + Extends a standard Overlay Action-Object by + a. refining update to ONLY accept SchemaRestriction + b. letting the API provider pre-compute exactly which nodes will be + affected, using either JSON Pointers or OpenAPI runtime expressions. + This makes it possible to: + 1. **target** an OpenAPI document fragment (via JSONPath). + 2. **Resolve** that target against an instance of the Open API schema + into one or more concrete locations—each expressed as either a JSON Pointer + or an OpenAPI runtime expression. + 3. **Apply** the `update` or `remove` action deterministically to those + resolved locations. + By including `targetLocations`, clients can skip the extra step of evaluating + `target` themselves against instances of the schema, ensuring precise, + unambiguous application and enabling robust validation through attached `SchemaRestrictions`. + When targetLocations is present, any target value MUST be ignored. + allOf: + - $ref: '#/components/schemas/Action' + properties: + id: + type: string + description: Identifier for this action. Used for tracability. Each id MUST + be unique within the overlay. + targetLocations: + description: | + A non-empty list of explicit document locations—specified as a + InstanceLocation. These values override the generic `target` + selector. + + All entries MUST use the same syntax (Runtime Expression or JSON Pointer). + type: array + minItems: 1 + maxItems: 30 + items: + $ref: '#/components/schemas/InstanceLocation' + # refinement of update - it can only take on + update: + description: update of schema restrictions + type: object + additionalProperties: + $ref: '#/components/schemas/SchemaRestrictions' + instanceUpdate: + description: An update of an instance document's value. + type: object + instanceRemove: + description: A boolean indicating the result's value should be removed from + the instance's document. + type: boolean + forceAction: + type: boolean + description: | + When **true**, and **restrictions** are satisfied, the specified + **instanceUpdate** or **instanceRemove** MUST be enforced (no silent failures). + If **forceAction** is present, either **instanceUpdate** or **instanceRemove** + MUST also be present. + default: true + example: true + # validation logic + anyOf: # target or targetLocations MUST be present + - required: [target] + - required: [targetLocations] + not: # instanceUpdate and instanceRemove MUST NOT be present at the same time + required: [instanceUpdate, instanceRemove] + # When forceAction is present, instanceUpdate or instanceRemove MUST be present + oneOf: + # Case A: forceAction is *not* present (nothing else enforced) + - not: + required: [forceAction] + # Case B: forceAction *is* present, and exactly one payload must accompany it + - allOf: + - required: [forceAction] + - oneOf: + - required: [instanceUpdate] + - required: [instanceRemove] + InstanceLocation: + description: | + A location in the JSON document that is an instance of an OpenAPI Schema. + It provides an optional endpoint to restrict it as well as the location. + All strings follow a Open API Runtime Expression or JSON Pointer (RFC 6901) format. + type: object + properties: + endpoint: + description: Optional endpoint path of a URI that MUST be present in the + request/response. + allOf: + - $ref: '#/components/schemas/InstanceLocationSyntax' + location: + description: The location of the target result. + allOf: + - $ref: '#/components/schemas/InstanceLocationSyntax' + additionalProperties: false + required: [location] + InstanceLocationSyntax: + description: A string whose format is Open API Runtime Expression or JSON Path. + type: string + minLength: 1 + oneOf: + - x-camara-targetSyntax: runtimeexpression # runtime expression + pattern: ^\$(?:url|method|statusCode|request\.(?:header\.[!#$%&'*+\-\.\^_`|~0-9A-Za-z]+|query\.[^\s\/]+|path\.[^\s\/]+|body(?:#\/(?:[^\/~]|~0|~1)+(?:\/(?:[^\/~]|~0|~1)+)*)?)|response\.(?:header\.[!#$%&'*+\-\.\^_`|~0-9A-Za-z]+|body(?:#\/(?:[^\/~]|~0|~1)+(?:\/(?:[^\/~]|~0|~1)+)*)?)) + minLength: 1 + - x-camara-targetSyntax: jsonPointer # JSON Pointer + pattern: ^(/([^/~]|~[01])*)*$ + minLength: 1 + SchemaRestrictions: + description: | + A set of schema constraints evaluated against a single target. + - **restrictions** - An array (min = 1) of `SchemaRestriction` objects. + Each restriction returns a Boolean result when applied to the target. + - **operator** - Optional logical operator that combines the restriction + results. Supported values are: **and** (default), **or**, **not**. + When a single restrictions is supplied, **not** negates that result. + If `operator` is omitted, **and** is assumed. + If only one restriction is present, `operator: not` will negate it. Values of `operator: and` and + `operator: or` are ignored. + If `operator` is present, `restrictions` **MUST** also be present. + type: object + properties: + restrictions: + description: An array of `SchemaRestriction` objects. + type: array + minItems: 1 + uniqueItems: true + items: + $ref: '#/components/schemas/SchemaRestriction' + operator: + description: | + Logical operator that combines the results of all restrictions. + - **and** - All restrictions MUST be true. + - **or** - At least one restriction MUST be true. + - **not** - No restriction MAY be true. For a single restriction this simply negates the result. + type: string + enum: [and, or, not] + default: and + required: [restrictions] + SchemaRestriction: + description: | + Single schema update that refines and restricts the target. + This update **MUST** be compatible with the referenced target. + type: object + anyOf: + - $ref: '#/components/schemas/SchemaRestrictionMeta' + - $ref: '#/components/schemas/SchemaRestrictionAnyInstance' + - $ref: '#/components/schemas/SchemaRestrictionNumeric' + - $ref: '#/components/schemas/SchemaRestrictionString' + - $ref: '#/components/schemas/SchemaRestrictionArray' + - $ref: '#/components/schemas/SchemaRestrictionObject' + - $ref: '#/components/schemas/SchemaRestrictionParameter' + - $ref: '#/components/schemas/SchemaRestrictionOperation' + - $ref: '#/components/schemas/SchemaRestrictionPresence' + SchemaRestrictionMeta: + type: object + description: > + Restriction applicable to any target at runtime. + Based upon the JSON Schema [A Vocabulary for Basic Meta-Data Annotations](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-a-vocabulary-for-basic-meta). + additionalProperties: false + properties: + deprecated: {type: boolean, description: Mark as deprecated.} + readOnly: {type: boolean, description: Mark as read-only.} + writeOnly: {type: boolean, description: Mark as write-only.} + default: {type: string, description: Default value to apply.} + SchemaRestrictionAnyInstance: + type: object + description: > + Restriction applicable to any target at runtime. + Based upon the JSON Schema [Validation keywords for Any instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-any). + additionalProperties: false + properties: + type: + type: string + enum: [boolean, object, array, number, string, integer] + nullable: true + description: > + Restrict the type of the value. Only applicable when the type was + not initially specified or matches the target's current type. + enum: + type: array + items: {type: string} + description: Restrict allowed values (must be a subset of the original enum). + const: + type: string + description: Force the field to have a constant value. + SchemaRestrictionNumeric: + type: object + description: > + Restriction applicable to numeric ranges (for example min/max values). + Based upon the JSON Schema [Validation keywords for Numeric Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-num). + additionalProperties: false + properties: + multipleOf: {type: number, minimum: 1, description: Value MUST be a multiple + of this number.} + maximum: {type: number, description: Value MUST be less than or equal to this + number.} + minimum: {type: number, description: Value MUST be greater than or equal to + this number.} + exclusiveMaximum: {type: number, description: Value MUST be strictly less + than this number.} + exclusiveMinimum: {type: number, description: Value MUST be strictly greater + than this number.} + SchemaRestrictionString: + type: object + description: > + Restriction applicable to string fields (length or pattern). + Based upon the JSON Schema [Validation keywords for Strings](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-str). + additionalProperties: false + properties: + maxLength: {type: integer, minimum: 0, description: Maximum string length.} + minLength: {type: integer, minimum: 0, description: Minimum string length.} + pattern: {type: string, description: Regular-expression pattern the string + MUST match.} + SchemaRestrictionArray: + type: object + description: > + Restriction applicable to arrays (size or uniqueness). + Based upon the JSON Schema [Validation keywords for Array Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-arr). + additionalProperties: false + properties: + maxItems: {type: integer, minimum: 0, description: Maximum number of items.} + minItems: {type: integer, minimum: 0, description: Minimum number of items.} + uniqueItems: {type: boolean, description: 'If **true**, all items MUST be + unique.'} + maxContains: {type: integer, minimum: 0, description: Maximum count for items + that match the `contains` schema.} + minContains: {type: integer, minimum: 0, description: Minimum count for items + that match the `contains` schema.} + SchemaRestrictionObject: + type: object + description: > + Restriction applicable to object structures. + Based upon the JSON Schema [Validation keywords for Object Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-obj). + additionalProperties: false + properties: + maxProperties: {type: integer, minimum: 0, description: Maximum number of + object properties.} + minProperties: {type: integer, minimum: 0, description: Minimum number of + object properties.} + required: + type: array + items: {type: string} + description: List of required properties (MUST already exist in the schema). + dependentRequired: + type: array + items: {type: string} + description: '[`dependentRequired`](https://json-schema.org/draft/2020-12/json-schema-validation#name-validation-keywords-for-obj)' + excludedProperties: + type: array + items: {type: string} + description: Properties that MUST be absent. + SchemaRestrictionParameter: + type: object + description: > + Restriction that applies only to HTTP request parameters (e.g. query + parameters). + Based upon the OpenAPI *Parameter Object* and provides: + - Mandating the use of an optional parameter - Allowing empty values + additionalProperties: false + properties: + allowEmptyValue: + type: boolean + description: > + Permits empty values. MAY be **true** only if the original schema + did not explicitly specify `allowEmptyValue: false`. + mandatory: + type: boolean + description: > + Mandates the use of an otherwise-optional parameter. Allowed only + when: 1. The original schema does **not** declare `deprecated: true`, + and 2. The original schema does **not** set `mandatory` to the opposite + value. + SchemaRestrictionOperation: + type: object + description: > + Restriction that applies to an absolute or relative path (operation). + Based upon the OpenAPI *Operation Object* and provides: + - `notImplemented` - `notAvailable` + additionalProperties: false + properties: + notImplemented: + type: boolean + description: Marks the operation as unimplemented. Invocation MUST return + **501 Not Implemented**. + notAvailable: + type: boolean + description: Marks the operation as temporarily unavailable. Invocation + MUST return **503 Service Unavailable**. + SchemaRestrictionPresence: + type: object + description: > + Restriction that applies to runtime presence of the target. + properties: + presence: + type: boolean + description: > + When **true**, at least one instance matching the target JSON Pointer + or JSON Path **MUST** be present. When **false**, no such instance **MAY** + be present. + SchemaRestrictionsSet: + description: Base restriction type + type: object + allOf: + - $ref: '#/components/schemas/VersionedName' + properties: + restrictions: + description: restrictions + type: array + uniqueItems: true + minItems: 1 + maxItems: 10 + items: + $ref: '#/components/schemas/CamaraOverlay' + footprints: + description: footprints + type: array + uniqueItems: true + minItems: 1 + maxItems: 10 + items: + $ref: '#/components/schemas/Footprint' + resourceServers: + description: resourceServers + type: array + uniqueItems: true # no duplicates + maxItems: 10 + items: + type: string + format: uri # ensures each locator is a valid URI + required: [restrictions] + + # Camara capability structures + CapabilityBitmap: + description: Common attributes of CAMARA capability bitmap + type: object + allOf: + - $ref: '#/components/schemas/CamaraCapabilityQuery' + properties: + mappingVersion: + type: string + description: Version of the capability to restriction mapping, used to detect + changes. + example: 1.0.0 + camaraCapabilitiesBitmap: + description: | + Bitmap value of the capabilities to show current state (active or inactive) of the RestrictionSet. + Decimal representation of a binary bitmask indicating active capabilities. + This integer should be interpreted as a binary string (bitfield), where: + - The **least significant bit (rightmost bit)** corresponds to key **"0"** in the `bitmapCapabilities` object. + - The next bit to the left corresponds to key **"1"**, and so on. + - Bit at position `n` (counting from right, 0-based) maps to key `"n"`. + For example: + - If `CapabilityBitmap` = `13`, the binary form is `1101`. + - Interpreted as: + - Bit 0 (LSB, rightmost) → "0" → active + - Bit 1 → "1" → inactive + - Bit 2 → "2" → active + - Bit 3 (MSB) → "3" → active + - This means `bitmapCapabilities["0"]`, `["2"]`, and `["3"]` apply. + Implementors of API provider should preserve this bit order when interpreting or generating the bitmask, so that capability indices remain consistent over time. + type: integer + minimum: 0 + format: int64 + maximum: 18446744073709551615 + example: 6 + required: [mappingVersion, camaraCapabilitiesBitmap] + CapabilityInfo: + description: A list of CapabilityDetail. + type: object + properties: + details: + description: a list of CapabilityDetail. + type: array + minItems: 1 + maxItems: 1000 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CapabilityDetail' + CapabilityDetail: + description: | + A self-contained snapshot of what each capability means (CapabilityBitmap) and its current active/inactive state. + When these are CapabilitySetFootprint the state is always active. + When it is CapabilitySetBitmap, then CapabilityBitmap is included that conveys the active/inactive state of each + bit position. + type: object + anyOf: + - $ref: '#/components/schemas/CapabilitySetFootprint' + - allOf: + - $ref: '#/components/schemas/CapabilitySetBitmap' + - $ref: '#/components/schemas/CapabilityBitmap' + minProperties: 1 + CapabilitySetFootprint: + description: | + Associates a capability with one or more RestrictionSets that + defined by footprint constraints. + type: object + additionalProperties: false # reject typos / undocumented fields + allOf: + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + properties: + footprints: + description: An array of restrictions that apply when the endpoint is present + in one of the entry's footprints. + type: array + minItems: 1 + maxItems: 64 + uniqueItems: true + items: + allOf: + - $ref: '#/components/schemas/SchemaRestrictionsSet' + - required: [footprints] + required: [footprints] + CapabilitySetBitmap: + description: | + Associates a capability with one or more RestrictionSets + define through a bitmap position. + type: object + allOf: + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + properties: + bitmapCapabilities: + type: object + description: > + Map of bitPosition → SchemaRestrictionsSet. Keys are stringified bitPosition + indices (duplicates impossible). **Header names (object keys)** SHOULD + consist of one or more digits, matching `^[0-9]+$`. (Note: OpenAPI 3.0.3 + cannot enforce key-name patterns natively.) + additionalProperties: + $ref: '#/components/schemas/SchemaRestrictionsSet' + required: [bitmapCapabilities] + + # API related information + CamaraCapabilityQueryRequest: + description: A list of queries in the request. + type: object + additionalProperties: true + properties: + queries: + description: A list of CamaraCapabilityQuery + type: array + minItems: 1 + maxItems: 100 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CamaraCapabilityQuery' + subscriptionRequest: + $ref: '#/components/schemas/CamaraExtendedSubscriptionRequest' + required: [queries] + CamaraCapabilityQuery: + description: Common attributes of CAMARA capability query + type: object + properties: + resourceScopes: + $ref: '#/components/schemas/ResourceScopes' + overlayExtends: + description: list of unique overlay extends in the query + type: array + minItems: 1 + maxItems: 20 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/Extends' + required: [overlayExtends] + ResourceScopes: + $ref: ../common/CAMARA_common.yaml#/components/schemas/ResourceScopes + ErrorInfo: + $ref: ../common/CAMARA_common.yaml#/components/schemas/ErrorInfo + + # Event structures + CamaraExtendedSubscriptionRequest: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraExtendedSubscriptionRequest + org.camaraproject.capability.v0.detail: + description: The detail of the requested capability event subscription. + type: object + allOf: + - $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/SubscriptionDetail + - type: object + properties: + resourceScopes: + $ref: '#/components/schemas/ResourceScopes' + additionalProperties: false + CloudEvent: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraExtendedCloudEventsAttribute + CloudEventData: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraCloudEventData + org.camaraproject.capability.v0.capability-bitmap-changed: + description: Event structure for capability bitmap changed + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/org.camaraproject.capability.v0.capability-bitmap-changed.data' + required: [data] + additionalProperties: false + example: + $ref: '#/components/examples/EVENT_CAPABILITY_BITMAP_CHANGED_EXAMPLE/value' + org.camaraproject.capability.v0.capability-bitmap-changed.data: + description: Event for capability bitmap changed + allOf: + - $ref: '#/components/schemas/CloudEventData' + - type: object + properties: + capabilityBitmap: + $ref: '#/components/schemas/CapabilityBitmap' + required: [capabilityBitmap] + additionalProperties: false + org.camaraproject.capability.v0.capability-info-changed: + description: Event structure for capability info changed + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/org.camaraproject.capability.v0.capability-info-changed.data' + required: [data] + additionalProperties: false + example: + $ref: '#/components/examples/EVENT_CAPABILITY_INFO_CHANGED_EXAMPLE/value' + org.camaraproject.capability.v0.capability-info-changed.data: + description: Event for capability info changed + allOf: + - $ref: '#/components/schemas/CloudEventData' + - type: object + properties: + capabilityInfo: + $ref: '#/components/schemas/CapabilityInfo' + required: [capabilityInfo] + additionalProperties: false + responses: + CapabilityNotModified304: + description: Not Modified (cached response) + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Generic400: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic400 + CapabilityApiBadRequest400: + description: Bad Request when query capability + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + title: CapabilityApiBadRequest400 + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: [400] + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query + param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given + field has a pre-defined range or a invalid filter criteria combination + is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + Generic401: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic401 + Generic403: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic403 + Generic404: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic404 + CapabilityApiNotFound404: + description: Capability API not found + content: + application/json: + schema: + title: CapabilityApiNotFound404 + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: [404] + code: + enum: [NOT_FOUND] + example: + status: 404 + code: NOT_FOUND + message: No Capability API found + Generic409: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic409 + Generic410: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic410 + Generic429: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic429 + Generic500: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic500 + Generic503: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic503 + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE: + summary: Example of capability query + description: query capability request + value: + queries: + - resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + subscriptionRequest: + sink: https://application-server.com/notifications + protocol: HTTP + types: + - org.camaraproject.capability.v0.capability-info-changed + - org.camaraproject.capability.v0.capability-bitmap-changed + config: + subscriptionDetail: + resourceScopes: + - phoneNumber: '+123456788' + CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE: + summary: Example of capability query response + description: query capability response + value: + details: + - name: cap-qod-adi + version: 1.0.1 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 63 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true + '1': + name: rr-qod-xcor + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.parameter-restriction.x-cor-required + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.parameters['x-correlator'] + update: + xcor-required: + restrictions: + - mandatory: true + '2': + name: rr-session-extend-unavailable + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.operation-restriction.session-extend-unavailable + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.paths['/sessions/{sessionId}/extend'].post + update: + session-extend-unavailable: + restrictions: + - notAvailable: true + '3': + name: rr-session-accept-qos + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.enum-restriction.accepted-qos-profiles + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + operator: and + actions: + - targetLocations: + - location: $method + update: + accepted-qos-profiles: + restrictions: + - enum: [POST] + - targetLocations: + - location: $request.path.sessionId + update: + accepted-qos-profiles: + restrictions: + - enum: [/sessions] + - targetLocations: + - location: $request.body#/qosProfile + update: + accepted-qos-profiles: + restrictions: + - enum: [QoS_XR, QoS_VC] + '4': + name: rr-ipv6-portspec-max-5 + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.appserv-ipv6 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['ApplicationServer'].properties['ipv4Address'] + remove: true + - name: org.camaraproject.capability.v0.array-size-restriction.portspec-ports-max5 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['PortsSpec'].properties['ports'] + update: + portspec-ports-max5: + restrictions: + - maxItems: 5 + '5': + name: rr-sessioninfo-duration-multipleof-60 + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.numeric-restriction.sessioninfo-duration-min60-multiple60 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['SessionInfo'].properties['duration'] + update: + sessioninfo-duration-min60-multiple60: + restrictions: + - minimum: 60 + - multipleOf: 60 + '6': + name: rr-qosprofile-get-unavailable + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.operation-restriction.qosprofile-get-unavailable + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + actions: + - target: $.paths['/qos-profiles/{name}'].get + remove: true + EVENT_CAPABILITY_BITMAP_CHANGED_EXAMPLE: + summary: Cloud event example for capability bitmap changed + description: Cloud event example for capability bitmap changed + value: + id: cb1 + source: https://api.example.com/capability/capability-subscriptions/bitmap + datacontenttype: application/json + specversion: '1.0' + type: org.camaraproject.capability.v0.capability-bitmap-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityBitmap: + resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 127 + EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE: + summary: Batch (single item) - capability bitmap changed + description: Cloud event batch example for capability bitmap changed + value: + - id: cb1 + source: https://api.example.com/capability/capability-subscriptions/bitmap + datacontenttype: application/json + specversion: '1.0' + type: org.camaraproject.capability.v0.capability-bitmap-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityBitmap: + resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 127 + EVENT_CAPABILITY_INFO_CHANGED_EXAMPLE: + description: Cloud event example for capability info changed + value: + id: ci1 + source: https://api.example.com/capability/capability-subscriptions/info + specversion: '1.0' + datacontenttype: application/json + type: org.camaraproject.capability.v0.capability-info-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityInfo: + details: + - name: cap-qod-adi + version: 1.0.2 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 1 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true + EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE: + summary: Batch (single item) - capability info changed + description: Cloud event batch example for capability info changed + value: + - id: ci1 + source: https://api.example.com/capability/capability-subscriptions/info + specversion: '1.0' + datacontenttype: application/json + type: org.camaraproject.capability.v0.capability-info-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityInfo: + details: + - name: cap-qod-adi + version: 1.0.2 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 1 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true +``` diff --git a/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aa6c387f8b2a24e6906cacb6fea498ccebe2d982 --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories/raw.md @@ -0,0 +1,26 @@ + +**User Story: Capabilities and Runtime Restrictions - Query** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want my application to comply with current restrictions applicable based on the service status, network conditions, and location | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Mobile Network Operators (MNO), [Entprerise] Application developers.
      **Scope:** Any device serviced by MNO| +| ***Pre-conditions*** |The preconditions are listed below:
      1. Application developer has been onboarded to MNO
      2. MNO offeres Capabilities and Runtime Restrictions APIs
      3. Application developer has subscribed to Capabilities and Runtime Restriction APIs
      4. As necessary, customer consent has been secured
      5. Application developer has implemented Capabilities and Runtime Restriction API
      | +| ***Activities/Steps*** | **Starts when:** Presumably upon mobile application client session start. Application makes a request to retreieve the list of capabilities, their status (enabled/disabled), and restrictions that are applicable to those enabled services, given a particular client.
      **Ends when:** MNO returns the capabilities and runtime restrictions applicable to the request.| +| ***Post-conditions*** |
      1. Application may adjust UI elements according to the current restrictions. The Application, when sending a request to the CAMARA API, can ensure / adjusts information according to the restrictions.
      2. MNO may maintain a cache of the capabilities and restrictions sent in response to Application request.
      | +| ***Exceptions*** | Several exceptions might occur:
      • Unauthorized: Not valid credentials
      • Not found: Client identifier is not managed by the MNO
      • Invalid Input: Request is not properly structured, or missing mandatory input data
      • Service not available: Capabilities and Runtime Restrictions service is [temporarily] not available
      | + +

      + +**User Story: Capabilities and Runtime Restrictions - Subscription** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want my application to comply with current restrictions applicable based on the service status, network conditions, and location. I want my application to subscribe to any changes in capabilities and restrictions | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Mobile Network Operators (MNO), [Entprerise] Application developers.
      **Scope:** Any device serviced by MNO| +| ***Pre-conditions*** |The preconditions are listed below:
      1. Application developer has been onboarded to MNO
      2. MNO offeres Capabilities and Runtime Restrictions APIs
      3. Application developer has subscribed to Capabilities and Runtime Restriction APIs
      4. As necessary, customer consent has been secured
      5. Application Client or the Application Backend server has implemented Capabilities and Runtime Restriction API
      | +| ***Activities/Steps*** | **Start when:** Presumably upon mobile application client session start. Application makes a request to receive the current the list of capabilities, their status (enabled/disabled), and restrictions that are applicable to those enabled services and subscribe to any changes after the intial push.
      **Continues with:**
      • Any changes in capabilities or runtime restrictions change sent as an event notification to subscribed Application
      • Application may adjust UI elements according to the current restrictions. The Application, when sending a request to the CAMARA API, can ensure / adjusts information according to the restrictions.
      **Ends when:** Subscrption expires, or subscribing entity terminates the subscription| +| ***Post-conditions*** |
      1. MNO may maintain a cache of the capabilities and restrictions responded with.
      2. Application client may enable/disable UI components based on restricted services at time.
      3. Application client validates, localy or with the Application backend server, Service API prior to making a request to the MNOs Service API endpoint, and avoids any failures.
      | +| ***Exceptions*** | Several exceptions might occur:
      • Unauthorized: Not valid credentials
      • Not found: Client identifier is not managed by the MNO
      • Invalid Input: Request is not properly structured, or missing mandatory input data
      • Service not available: Capabilities and Runtime Restrictions service is [temporarily] not available
      | diff --git a/marked/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README/raw.md b/marked/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/CarrierBillingCheckOut/README/raw.md b/marked/CarrierBillingCheckOut/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..57ed3697d4baf544e7207047c92804ec257cfb4a --- /dev/null +++ b/marked/CarrierBillingCheckOut/README/raw.md @@ -0,0 +1,58 @@ + + + + + + + + + +# CarrierBillingCheckOut + +Sandbox API Repository to describe, develop, document, and test the CarrierBillingCheckOut Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/CDDe) + +## Scope +* Service APIs for “CarrierBillingCheckOut” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Trigger carrier billing payment request (in one or two steps), which is a process that allows API consumers to make purchases by charging payments against Telco Operator Billing Systems. + * Follow up of payment, by means of query endpoints to get information about a list of payments or a specific payment. + * Trigger carrier billing refund request, which is a process that allows API consumers to ask for a `total` or `partial` return of the amount associated to a previous performed payment. + * Follow up of refund, by means of query endpoints to get information about a list of refunds or a specific refund. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/r3.2) (Fall25), with the following API versions: + * **carrier-billing-refund v0.3.0** + [[YAML]](https://github.com/camaraproject/CarrierBillingCheckOut/blob/r3.2/code/API_definitions/carrier-billing-refund.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing-refund.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing-refund.yaml) + * **carrier-billing v0.5.0** + [[YAML]](https://github.com/camaraproject/CarrierBillingCheckOut/blob/r3.2/code/API_definitions/carrier-billing.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CarrierBillingCheckOut/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CarrierBillingCheckOut/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly, Wednesdays 13:00 - 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96513497117?password=ac26d34b-87d2-4d78-aa47-4de1ca14c882) + * Minutes: Access [Meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/CDDe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund/raw.md b/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7c49edb648ea5c1ce844d02c58af1737a6a9d69a --- /dev/null +++ b/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund/raw.md @@ -0,0 +1,1417 @@ +# carrier-billing-refund + +```yaml +openapi: 3.0.3 +info: + description: |- + Service Enabling Refunds against Operator Carrier Billing Systems + + # Introduction + + The Carrier Billing Refund API provides programmable interface for developers and other users (capabilities consumers) to perform a refund over a given payment. + The API provides management of a refund entity and its associated lifecycle. + + # Relevant terms and definitions + + - **Carrier Billing**: + An online payment process which allows users to make purchases by charging payments against Telco Operator Billing Systems, accordingly to the user's configuration in the Telco Operator. In a common usage in the industry, the payment is processed on current account balance or charged on next bill generated for this line. + + - **Payment**: + The process of paying for a (set of) good(s)/service(s). + + - **Refund**: + The process of returning the amount involved in a given payment (totally or partially) back to the user. + + # API Functionality + + This API allows to third party clients to request the refund of a given payment, as well as to retrieve information about a specific refund or a list of refunds. + + The API provides several endpoints/operations: + - An endpoint to request a refund, named `createRefund`. + - A set of endpoints to retrieve information about a list of refunds or a specific refund (identified by its specific `refundId`), named `retrieveRefunds` and `retrieveRefund` respectively. + - A callback endpoint where API Server can send notifications about a refund procedure, as defined within `createRefund` operation, towards the `sink` when provided by API client. + - An endpoint to retrieve remaining amount on a payment taken into consideration processed refund, named `retrievePaymentRemainingAmount`. + + State transitions: + + If `createRefund` is a **SYNC** process: + - Response contains `refundId` and refundStatus=`succeeded`. + - In case of any error scenario `refundId` is not created. + + If `createRefund` is an **ASYNC** process: + - Response contains `refundId` and refundStatus=`processing`. After completion: + - When refund is successfully completed then refundStatus=`succeeded`. + - When refund is not successfully performed then refundStatus=`denied`. + - In case of any error scenario `refundId` is not created. That means a `denied` Refund is not considerated as an error for the ASYNC process, because a `denied` Refund is a refund that has been created (i.e. the refund resource exists) and after applying the internal business logic has been settled to `denied` refundStatus. + + # Generic Clarification about optional parameters + + Regarding optional parameters, they can be conditionally mandatory for a Telco Operator to implement them based on business scenarios or applicable regulations in a given market. + + NOTE: Within a given market, in a multi Telco Operator ecosystem, the set of optional parameters to be implemented MUST be aligned among involved Telco Operators. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Carrier Billing Refund + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/CarrierBillingCheckOut +servers: + - url: "{apiRoot}/carrier-billing-refund/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Refund + description: Operations to manage Refund procedure +paths: + /payments/{paymentId}/refunds: + post: + security: + - openId: + - carrier-billing-refund:refunds:create + tags: + - Refund + summary: Create a new Refund + operationId: createRefund + description: Create a new refund for an existing payment. Refund can be `total` or `partial`. This procedure MUST be always limited to the API client which performed the related payment. + parameters: + - name: paymentId + in: path + description: The payment identifier for which the payment refund is requested. + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Refund transaction + content: + application/json: + schema: + $ref: "#/components/schemas/CreateRefund" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Refund Notifications + summary: Carrier Billing refund notifications + operationId: createRefundNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing refund notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Refund" + "400": + $ref: "#/components/responses/RefundInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/RefundPermissionDenied403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/CreateRefundUnprocessableContent422" + "409": + $ref: "#/components/responses/Generic409" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get a list of refunds + operationId: retrieveRefunds + description: |- + Retrieve a list of refunds and their details for a specific payment, identified by its `paymentId`, based on some filtering criteria. + Regardless the refund criteria provided, response MUST be always limited to refunds performed by the API client (i.e same oAuth credentials) triggering this request. + This is to guarantee no API client can check refunds performed by other, therefore avoiding any legal or privacy topic. + + When Access Token is issued for a given user phone number, the list of refunds returned would be only the ones associated to that user phone number and API client. When Access Token is not associated to a user phone number, therefore only associated to API client the list of refunds returned would be all the ones managed by that API client. + + Considerations regarding `refundCreationDate.gte`, `refundCreationDate.lte`: + - If both included, return refunds in that date range + - If no one included, no filtering by date range is applied + - If only settled `refundCreationDate.gte`, `refundCreationDate.lte` is considered current date-time + - If only settled `refundCreationDate.lte`, every refund existing in the Operator billing system until such date is returned + parameters: + - name: paymentId + in: path + description: Payment identifier for which their refunds are queried + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Page" + - $ref: "#/components/parameters/PerPage" + - $ref: "#/components/parameters/StartRefundCreationDate" + - $ref: "#/components/parameters/EndRefundCreationDate" + - $ref: "#/components/parameters/Order" + - $ref: "#/components/parameters/RefundStatus" + - $ref: "#/components/parameters/MerchantIdentifier" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: "#/components/schemas/RefundArray" + "400": + $ref: "#/components/responses/GetRefundsInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/refunds/{refundId}: + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get refund details + operationId: retrieveRefund + description: |- + Retrieve refund details for a given refund. + + When Access Token is issued for a given user phone number, the refund details would be returned in case the `refundId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the refund details are returned in case the API client managed that refund. + parameters: + - name: paymentId + in: path + description: Payment identifier associated to the `refundId` + required: true + schema: + type: string + - name: refundId + in: path + description: Refund identifier that was obtained from the create refund operation + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Refund" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/refunds/remaining-amount: + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get remaining amount not refunded for a given payment + operationId: retrievePaymentRemainingAmount + description: |- + Retrieve remaining amount not yet refunded for a given payment. This amount refers to the pending amount never requested to be refunded (i.e. a refund not yet consolidated -processing- implies that such an amount is not part of the remaining amount until final status for that procedure is reached). Some cases below to illustrate the behaviour: + + **Case_1:** Payment of 80 EUR, with 2 partial `succedeed` Refunds, each of them of 20 EUR + - remainingAmount: 40 EUR + + **Case_2:** Payment of 80 EUR, with 2 partial Refunds, one `succeeded` of 20 EUR and other `processing` of 15 EUR + - remainingAmount: 45 EUR (API cannot return 60 EUR, because there is an ongoing refund process) + + ***SubCase_A***: Second partial Refund of 15 EUR is `succeeded` + - remainingAmount: 45 EUR + + ***SubCase_B***: Second partial Refund of 15 EUR is `denied` + - remainingAmount: 60 EUR + + **Case_3:** Payment of 80 EUR, with 1 total `succeeded` Refund + - remainingAmount: 0 EUR + + **Case_4:** Payment of 80 EUR, with 1 total `processing` Refund + - remainingAmount: 0 EUR (API cannot return 80 EUR, because there is an ongoing refund process) + + ***SubCase_A***: Total Refund is `succeeded` + - remainingAmount: 0 EUR + + ***SubCase_B***: Total Refund is `denied` + - remainingAmount: 80 EUR + + When Access Token is issued for a given user phone number, information would be returned in case the `paymentId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the information is returned in case the API client managed that payment. + parameters: + - name: paymentId + in: path + description: Payment identifier associated to the `refundId` + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentRemainingAmount" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreateRefund: + type: object + description: Information to create a Refund resource. + required: + - type + properties: + type: + type: string + description: |- + Type of refund. + - `total` stands for a final refund, where whole amount is refunded so as it is not indicated by API Consumer. No more refunds are allowed for that `paymentId`. + - `partial` stands for a partial refund, whose amount is indicated by API Consumer. More refunds are allowed for that `paymentId`. + enum: + - total + - partial + reason: + type: string + description: Reason provided to request the refund. Optionally provided by the user or the merchant. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + discriminator: + propertyName: type + mapping: + total: "#/components/schemas/CreateTotalRefund" + partial: "#/components/schemas/CreatePartialRefund" + CreateTotalRefund: + allOf: + - $ref: "#/components/schemas/CreateRefund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionTotalRefund" + CreatePartialRefund: + allOf: + - $ref: "#/components/schemas/CreateRefund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionPartialRefund" + Refund: + type: object + description: Information about a Refund resource. + required: + - refundId + - refundStatus + - refundCreationDate + - type + properties: + refundId: + type: string + description: Unique Identifier of the refund + example: "AK234rfweSBuWGFUEWFGWEVWRV" + refundStatus: + type: string + description: Specifies the refund status (`processing`, `denied`, `succeeded`). + example: "processing" + type: + type: string + description: |- + Type of refund. + - `total` stands for a final refund, where whole amount is refunded so as it is not indicated by API Consumer. No more refunds are allowed for that `paymentId`. + - `partial` stands for a partial refund, whose amount is indicated by API Consumer. More refunds are allowed for that `paymentId`. + enum: + - total + - partial + refundCreationDate: + type: string + format: date-time + description: Date time when the refund is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + refundDate: + type: string + format: date-time + description: Date time when the refund is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + reason: + type: string + description: Reason provided to request the refund. Optionally provided by the user or the merchant. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + discriminator: + propertyName: type + mapping: + total: "#/components/schemas/TotalRefund" + partial: "#/components/schemas/PartialRefund" + TotalRefund: + allOf: + - $ref: "#/components/schemas/Refund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionTotalRefund" + PartialRefund: + allOf: + - $ref: "#/components/schemas/Refund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionPartialRefund" + AmountTransactionTotalRefund: + type: object + required: + - refundAmount + - referenceCode + properties: + clientCorrelator: + type: string + description: + Uniquely identifies this create refund request. If there is + a communication failure during the refund request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + refundAmount: + $ref: "#/components/schemas/RefundAmountTotalRefund" + referenceCode: + type: string + description: + Merchant generated refund reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-refund-834tfr2rA3v8r8vr3rv" + RefundAmountTotalRefund: + type: object + description: Information for a `total` refund. Whole amount is refunded so as it is not needed to be provided, then it can be an empty object unless `merchantIdentifier` is indicated. + properties: + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + AmountTransactionPartialRefund: + type: object + required: + - refundAmount + - referenceCode + properties: + clientCorrelator: + type: string + description: + Uniquely identifies this create refund request. If there is + a communication failure during the refund request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + refundAmount: + $ref: "#/components/schemas/RefundAmountPartialRefund" + referenceCode: + type: string + description: + Merchant generated refund reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-refund-834tfr2rA3v8r8vr3rv" + RefundAmountPartialRefund: + type: object + description: Information for a `partial` refund. Amount to be refunded is required. + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + refundDetails: + $ref: "#/components/schemas/RefundDetails" + RefundArray: + description: A list of refund(s) + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Refund" + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. Only `ACCESSTOKEN` is supported so far." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment refund, allowing the client to be notified of any changes during the payment refund's existence. If the token expires while the payment refund is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment refund, allowing the client to be notified of any changes during the payment refund's existence. If the token expires while the payment refund is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + ChargingInformation: + type: object + required: + - amount + - currency + - description + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Amount to be refunded. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingMetaData: + type: object + properties: + merchantIdentifier: + type: string + description: Indicates the merchant identifier. Allows aggregators/partners to specify the actual merchant identifier + example: "eas-12345" + RefundDetails: + type: array + description: Detailed description of the concepts/items considered within a specific refund procedure. + minItems: 1 + items: + $ref: "#/components/schemas/RefundItem" + RefundItem: + type: object + required: + - paymentItemId + - amount + - currency + - description + properties: + paymentItemId: + type: string + description: |- + Unique payment item identifier to which this refund item is related to. Relevant when indicating `refundDetails` to correlate information for a refund regarding this `paymentItemId`. + example: "3goug3uvu32v3b" + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Specific amount to be refunded referred to a specific item. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text referred to a specific item. + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + PaymentRemainingAmount: + type: object + description: Remaining Amount of a given payment not refunded yet. + required: + - amount + - currency + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: Specific amount not yet refunded for the payment. When takes value `0` it means whole payment has been refunded. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text (human readable) to contextualize this amount. Optionally indicated by Telco Operator. + example: "Current Amount not refunded so far" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + CloudEvent: + description: The notification format + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + minLength: 1 + example: "sd5e-uy52-88t4-za66" + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: Type of event as defined in each CAMARA API + minLength: 25 + example: "org.camaraproject.carrier-billing.v0.payment-reserved" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + minLength: 3 + example: "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: "application/json" + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.carrier-billing-refund.v0.refund-completed: "#/components/schemas/EventRefundCompleted" + org.camaraproject.carrier-billing-refund.v0.refund-denied: "#/components/schemas/EventRefundDenied" + org.camaraproject.carrier-billing-refund.v0.refund-in-bill: "#/components/schemas/EventRefundInBill" + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + DateTime: + type: string + format: date-time + description: Timestamp when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-11-03T12:27:10Z" + EventRefundCompleted: + description: Event structure for refund completed + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundCompleted" + EventRefundDenied: + description: Event structure for refund denied + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundDenied" + EventRefundInBill: + description: Event structure for refund in bill (i.e. confirmation about refund will be applied in next bill) + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundInBill" + RefundCompleted: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-completed event + - $ref: "#/components/schemas/BasicEvent" + - type: object + required: + - refundDate + properties: + refundDate: + type: string + description: Date when the refund is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + example: "2023-11-03T12:27:08.312Z" + RefundDenied: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-denied event + - $ref: "#/components/schemas/BasicEvent" + - type: object + properties: + denialReason: + type: string + description: Indicates the business reason for denying the refund. + example: "User is blocked due to pending debt" + RefundInBill: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-in-bill event + - $ref: "#/components/schemas/BasicEvent" + BasicEvent: + type: object + description: Data type to provide basic refund event information + required: + - paymentId + - refundId + - status + - description + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + refundId: + type: string + description: Unique Identifier of the refund + example: "AK234rfweSBuWGFUEWFGWEVWRV" + status: + type: string + enum: + - succeeded + - failed + description: |- + Status of the refund procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + example: "Payment Notification" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Invalid input + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GetRefundsInvalid400: + description: |- + Invalid input. In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Inconsistent refundCreationDate.gte and refundCreationDate.lte values ("code": "CARRIER_BILLING_REFUND.INVALID_DATE_RANGE","message": "Client specified an invalid date range."). + - Request out of range ("code": "OUT_OF_RANGE","message": "Client specified an invalid range."). + - Too many matching records found ("code": "CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS","message": "Too many matching records found. Specify additional/suitable criteria to limit the number of records."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - CARRIER_BILLING_REFUND.INVALID_DATE_RANGE + - CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_DATE_RANGE: + summary: Generic Invalid Date Range + description: Inconsistent refundCreationDate.gte and refundCreationDate.lte values + value: + status: 400 + code: CARRIER_BILLING_REFUND.INVALID_DATE_RANGE + message: "Client specified an invalid date range." + GENERIC_400_OUT_OF_RANGE: + summary: Generic Out Of Range + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_TOO_MANY_MATCHING_RECORDS: + summary: Generic Too Many Matching Records + description: Too many matching records found + value: + status: 400 + code: CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS + message: "Too many matching records found. Specify additional/suitable criteria to limit the number of records." + RefundInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - Currency is unknown or not authorized ("code": "INVALID_ARGUMENT","message": "Currency is unknown or not authorized."). + - clientCorrelator still exist ("code": "INVALID_ARGUMENT","message": "clientCorrelator already exist on server."). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_WRONG_CURRENCY: + summary: Generic Wrong Currency + description: Currency is unknown or not authorized + value: + code: INVALID_ARGUMENT + status: 400 + message: "Currency is unknown or not authorized." + GENERIC_400_DUPLICATE_CLIENT_CORRELATOR: + summary: Generic Duplicate Client Correlator + description: clientCorrelator still exist + value: + code: INVALID_ARGUMENT + status: 400 + message: "clientCorrelator already exist on server." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + RefundPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Refund denied by business ("code": "CARRIER_BILLING_REFUND.REFUND_DENIED","message": "Refund denied by business."). + - Payment not eligible for Refund (e.g. Payment conditions agreed do not allow refund) ("code": "CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND","message": "Payment not eligible for refund."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING_REFUND.REFUND_DENIED + - CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_REFUND_DENIED: + summary: Generic Refund Denied + description: Refund denied by business + value: + status: 403 + code: CARRIER_BILLING_REFUND.REFUND_DENIED + message: "Refund denied by business." + GENERIC_403_PAYMENT_NOT_ELIGIBLE_FOR_REFUND: + summary: Generic Payment Not Eligible for Refund + description: Payment not eligible for Refund (e.g. Payment conditions agreed do not allow refund) + value: + status: 403 + code: CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND + message: "Payment not eligible for refund." + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + summary: Generic Gone + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateRefundUnprocessableContent422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios considered: + - Unauthorized refund amount requested ("code": "CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT","message": "Unauthorized amount requested."). + - Accumulated threshold refund amount for the user's mobile account overpassed ("code": "CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED","message": "Unauthorized refund request. Accumulated user mobile refunds overpass account amount threshold."). + - Payment is not in suitable status for refund ("code": "CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS","message": "Payment is not yet completed."). + - Property `isTaxIncluded` has not the same value as related Payment ("code": "CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH","message": "Inconsistent isTaxIncluded value with regards to related payment."). + - Refund details provided are inconsistent with regards to the related Payment ("code": "CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH","message": "Inconsistent refundDetails information with regards to related payment."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT + - CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED + - CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS + - CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH + - CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH + examples: + GENERIC_422_UNAUTHORIZED_REFUND_AMOUNT: + summary: Generic Unauthorized Refund Amount + description: Unauthorized refund amount requested + value: + status: 422 + code: CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT + message: "Unauthorized amount requested." + GENERIC_422_GENERIC_422_USER_MOBILE_ACCUMULATED_THRESHOLD_REFUND_AMOUNT_OVERPASSED: + summary: Generic User Mobile Accumulated threshold Refund Amount Overpassed + description: Accumulated threshold refund amount for the user's mobile account overpassed + value: + status: 422 + code: CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED + message: "Unauthorized refund request. Accumulated user mobile payments overpass account amount threshold." + GENERIC_422_INVALID_PAYMENT_STATUS: + summary: Generic Invalid Payment Status + description: Payment is not in suitable status for refund + value: + status: 422 + code: CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS + message: "Payment is not yet completed." + GENERIC_422_TAXES_MANAGEMENT_MISMATCH: + summary: Generic Taxes Management Mismatch + description: Property `isTaxIncluded` has not the same value as related Payment + value: + status: 422 + code: CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH + message: "Inconsistent isTaxIncluded value with regards to related payment." + GENERIC_422_REFUND_DETAILS_MISMATCH: + summary: Generic Refund Details Mismatch + description: Refund details provided are inconsistent with regards to the related Payment + value: + status: 422 + code: CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH + message: "Inconsistent refundDetails information with regards to related payment." + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + summary: Generic Too Many Requests + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + default: 1 + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + default: 10 + StartRefundCreationDate: + description: Initial `refundCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: refundCreationDate.gte + required: false + schema: + format: date-time + type: string + EndRefundCreationDate: + description: End `refundCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: refundCreationDate.lte + required: false + schema: + format: date-time + type: string + Order: + description: Used to return the sorted results in descending (default) or ascending order, based on `refundCreationDate` property + in: query + name: order + required: false + schema: + default: desc + enum: + - desc + - asc + type: string + RefundStatus: + description: List of refund status to be considered for the query + in: query + name: refundStatus + required: false + schema: + type: array + items: + type: string + enum: + - processing + - denied + - succeeded + MerchantIdentifier: + description: Merchant identifier to filter the results + in: query + name: merchantIdentifier + required: false + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer +``` diff --git a/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing/raw.md b/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4c7ff0ec4ec6969dab352dbe27a8758867f6ecb2 --- /dev/null +++ b/marked/CarrierBillingCheckOut/code/API_definitions/carrier-billing/raw.md @@ -0,0 +1,2293 @@ +# carrier-billing + +```yaml +openapi: 3.0.3 +info: + description: |- + Service Enabling Payments against Operator Carrier Billing Systems + + # Introduction + + The Carrier Billing API provides programmable interface for developers and other users (capabilities consumers) to charge an amount on a mobile line. + It can be easily integrated and allows end-users to buy digital content in an easy & secured way. The API provides management of a payment entity and its associated lifecycle. + + # Relevant terms and definitions + + - **Carrier Billing**: + An online payment process which allows users to make purchases by charging payments against Telco Operator Billing Systems, accordingly to the user's configuration in the Telco Operator. In a common usage in the industry, the payment is processed on current account balance or charged on next bill generated for this line. + + - **Payment**: + The process of paying for a (set of) good(s)/service(s). + + - **1-STEP Payment**: + Payment process performed in one phase (i.e. one action), that involves all the Telco Operator Carrier Billing Systems checking and trigger the charging request against Billing Systems. + + - **2-STEP Payment**: + Payment process performed in two phases (i.e. two actions). First action deals with payment preparation request to guarantee the reservation of the involved amount. Second action is an explicit confirmation or cancellation of the payment by the user. Any payment not confirmed/cancelled by a given user is discarded after some time in order to avoid inconsistency in the billing systems. + + # API Functionality + + This API allows to third party clients to request the payment of a (set of) digital good(s)/service(s), as well as to retrieve information about a specific payment or a list of payments. + + In the scope of **version v0.5rc1, only one-off payments are covered**. Recurrent payments (a.k.a. payment subscriptions) are not covered so far. + + The API provides several endpoints/operations: + - An endpoint to request a 1-STEP Payment, named `createPayment`. + - A set of endpoints to request a 2-STEP Payment: + - One endpoint to setup the payment reservation, named `preparePayment`. + - A couple of endpoints to confirm/cancel such payment reservation, named `confirmPayment` and `cancelPayment` respectively. + - A set of endpoints to retrieve information about a list of payments or a specific payment (identified by its specific `paymentId`), named `retrievePayments` and `retrievePayment` respectively. + - A callback endpoint where API Server can send notifications about a payment procedure, as defined within `createPayment` and `preparePayment` operations, towards the `sink` when provided by API client. + + The usage of the API is based on Payment resource, which can be created (in 1-STEP or 2-STEP Payment process), confirmed/cancelled (for 2-STEP Payment process), and queried/retrieved (list of payments or a specific payment). + + Before starting to use the API, the developer needs to know about the below specified details: + - **Payment service endpoint**: The URL pointing to the RESTful resource of the payment API. As 1-STEP and 2-STEP processes are managed, 2 separate tags _`One Step Payment`_ and _`Two Step Payment`_ have been defined to explicitly distinguish them in the API specification. A third tag _`Payment`_ is defined for common operations in both processes (query/retrieve list of payments or a specific payment). + - **1-STEP & 2-STEP Payment**: + - **1-STEP Payment**: The request intent is to charge an amount to the mobile line. When the server receives the request, it will check the user account associated with this line and, if nothing prevents it, the amount is charged and will be either bill in next invoice or removed from current line credit/balance. + - **2-STEP Payment**: The first call is to request a payment preparation, which implies an amount reservation. The amount is not charged and the server has to be ready to get a confirmation or a cancellation to perform the payment. Only when the confirmation is done, payment is charged. Depending on business rules of the Telco operator, a `prepared` payment could expire after a defined delay. + - **Notification URL**: Developers may provide a callback URL (`sink` param) on which status change notifications, regarding the payment, can be received from the Telco Operator. This is an optional parameter. + + Following diagram shows the API resources operation sequencing: + ![PaymentSequence](https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/documentation/API_documentation/resources/Carrier_Billing_sequence_diagram.png) + + Follow picture provides information about the payment state engine (state description & transition): + ![Payment State Engine](https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/documentation/API_documentation/resources/Carrier_Billing_State_Engine.JPG) + + State transitions: + + **1-STEP Payment** + + If `createPayment` is a **SYNC** process: + - Response contains `paymentId` and paymentStatus=`succeeded`. + - In case of any error scenario `paymentId` is not created. + + If `createPayment` is an **ASYNC** process: + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment is successfully completed then paymentStatus=`succeeded`. + - When payment is not successfully performed then paymentStatus=`denied`. + - In case of any error scenario `paymentId` is not created. + + **2-STEP Payment** + + FIRST STEP + + If `preparePayment` is a **SYNC** process: + - **Case A** - `validationInfo` is NOT provided in response. + - Response contains `paymentId` and paymentStatus=`reserved`. + - **Case B** - `validationInfo` is provided in response. + - Response contains `paymentId` and paymentStatus=`pending_validation`. + - In case of any error scenario `paymentId` is not created. + + If `preparePayment` is an **ASYNC** process: + - **Case A** - `validationInfo` is NOT provided in response. + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment preparation is successfully completed then paymentStatus=`reserved`. + - When payment preparation is not successfully performed then paymentStatus=`denied`. + - **Case B** - `validationInfo` is provided in response. + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment preparation is successfully completed then paymentStatus=`pending_validation`. [1] + - When payment preparation is not successfully performed then paymentStatus=`denied`. + - In case of any error scenario `paymentId` is not created. + + [OPTIONAL] VALIDATE STEP [1] + + After `validatePayment`, paymentStatus=`reserved` OR `denied`, depending whether it was successful or not. + + SECOND STEP + + After `confirmPayment`, paymentStatus=`succeeded` OR `denied`, depending whether it was successful or not. + + After `cancelPayment`, paymentStatus=`cancelled`. + + # Generic Clarification about optional parameters + + Regarding optional parameters, they can be conditionally mandatory for a Telco Operator to implement them based on business scenarios or applicable regulations in a given market. + + NOTE: Within a given market, in a multi Telco Operator ecosystem, the set of optional parameters to be implemented MUST be aligned among involved Telco Operators. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Carrier Billing + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/CarrierBillingCheckOut +servers: + - url: "{apiRoot}/carrier-billing/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: One Step Payment + description: Operations to manage One Step Payment procedure + - name: Two Step Payment + description: Operations to manage Two Step Payment procedure + - name: Payment + description: Operations to obtain information about payments +paths: + /payments: + post: + security: + - openId: + - carrier-billing:payments:create + tags: + - One Step Payment + summary: Create a new Payment + operationId: createPayment + description: Create a new payment for subsequent charging to an end user. Carrier Billing Server will apply the charging according to business configuration for the end user. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: "#/components/schemas/CreatePayment" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Payment Notifications + summary: Carrier Billing payment notifications + operationId: createPaymentNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing payment notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentCreated" + "400": + $ref: "#/components/responses/PaymentInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentPermissionDenied403" + "404": + $ref: "#/components/responses/IdentifierNotFound404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/PaymentUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - carrier-billing:payments:read + tags: + - Payment + summary: Get a list of payments + operationId: retrievePayments + description: |- + Retrieve a list of payments and their details based on some filtering criteria. + Regardless the payment criteria provided, response MUST be always limited to payments performed by the API client (i.e same oAuth credentials) triggering this request. + This is to guarantee no API client can check payments performed by other, therefore avoiding any legal or privacy topic. + + When Access Token is issued for a given user phone number, the list of payments returned would be only the ones associated to that user phone number and API client. When Access Token is not associated to a user phone number, therefore only associated to API client the list of payments returned would be all the ones managed by that API client. + + Considerations regarding `paymentCreationDate.gte`, `paymentCreationDate.lte`: + - If both included, return payments in that date range + - If no one included, no filtering by date range is applied + - If only settled `paymentCreationDate.gte`, `paymentCreationDate.lte` is considered current date-time + - If only settled `paymentCreationDate.lte`, every payment existing in the Operator billing system until such date is returned + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Page" + - $ref: "#/components/parameters/PerPage" + - $ref: "#/components/parameters/StartPaymentCreationDate" + - $ref: "#/components/parameters/EndPaymentCreationDate" + - $ref: "#/components/parameters/Order" + - $ref: "#/components/parameters/PaymentStatus" + - $ref: "#/components/parameters/MerchantIdentifier" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentArray" + "400": + $ref: "#/components/responses/GetPaymentsInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}: + get: + security: + - openId: + - carrier-billing:payments:read + tags: + - Payment + summary: Get payment details + operationId: retrievePayment + description: |- + Retrieve payment details for a given payment. + + When Access Token is issued for a given user phone number, the payment details would be returned in case the `paymentId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the payment details are returned in case the API client managed that payment. + parameters: + - name: paymentId + in: path + description: Payment identifier that was obtained from the create payment operation + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Payment" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/prepare: + post: + security: + - openId: + - carrier-billing:payments:create + tags: + - Two Step Payment + summary: Prepare (reserve) a payment + operationId: preparePayment + description: Prepare a new payment procedure. Carrier Billing Server will apply the charging according to business configuration for the end user. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: "#/components/schemas/BodyAmountReservationTransactionForReserveInput" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Payment Notifications + summary: Carrier Billing payment notifications + operationId: preparePaymentNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing payment notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BodyAmountReservationTransactionForReserve" + "400": + $ref: "#/components/responses/Payment2StepPrepareInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentPermissionDenied403" + "404": + $ref: "#/components/responses/IdentifierNotFound404" + "409": + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + code: ALREADY_EXISTS + status: 409 + message: "Another session is created for the same UE" + "422": + $ref: "#/components/responses/PaymentUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/validate: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Validate a payment + operationId: validatePayment + description: Validate a given payment with a code, identified by its paymentId. This process is applicable for 2-STEP, when optionally required by business case. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + schema: + type: string + required: true + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Payment Validation + content: + application/json: + schema: + $ref: "#/components/schemas/ValidatePayment" + required: true + responses: + "204": + description: Validation Succeeded + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/ValidatePaymentInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Conflict + description: paymentId already validated + value: + code: ALREADY_EXISTS + status: 409 + message: "Payment already validated" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/confirm: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Confirm a payment + operationId: confirmPayment + description: Confirm a reservation of a given payment, identified by its paymentId. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + schema: + type: string + required: true + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: capture PhoneNumber for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "202": + description: Payment confirmation accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Payment2StepInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentConfirmPermissionDenied403" + "404": + $ref: "#/components/responses/Identifier2StepNotFound404" + "409": + $ref: "#/components/responses/PaymentConfirmConflict409" + "422": + $ref: "#/components/responses/PaymentSecondStepUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/cancel: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Cancel a payment + operationId: cancelPayment + description: Cancel a reservation of a given payment, identified by its paymentId. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: capture PhoneNumber for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "202": + description: Payment Cancellation Accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Payment2StepInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentCancelPermissionDenied403" + "404": + $ref: "#/components/responses/Identifier2StepNotFound404" + "409": + $ref: "#/components/responses/PaymentCancelConflict409" + "422": + $ref: "#/components/responses/PaymentSecondStepUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreatePayment: + type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionInput" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + PaymentCreated: + type: object + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountTransaction" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + paymentDate: + type: string + format: date-time + description: Date time when the payment is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + PaymentArray: + description: A list of payment(s) + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Payment" + Payment: + type: object + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountTransaction" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + paymentDate: + type: string + format: date-time + description: Date time when the payment is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. Only `ACCESSTOKEN` is supported so far." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment, allowing the client to be notified of any changes during the payment's existence. If the token expires while the payment is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment, allowing the client to be notified of any changes during the payment's existence. If the token expires while the payment is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + AmountTransaction: + required: + - phoneNumber + - paymentAmount + - referenceCode + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. Same value as indicated in the request. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForCharge" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. Same value as the one provided in the request. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + example: "urn:payments:AK234rfweSBuWGFUEWFGWEVWRV" + serverReferenceCode: + type: string + description: + Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + example: "ref-pay-834tfr2rA3v8r8vr3rv-serv" + AmountTransactionInput: + type: object + required: + - paymentAmount + - referenceCode + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForCharge" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + PaymentAmountForCharge: + type: object + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + paymentDetails: + $ref: "#/components/schemas/PaymentDetails" + PhoneNumber: + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + ValidatePayment: + type: object + required: + - authorizationId + - code + properties: + authorizationId: + type: string + description: Unique authorization identifier for a specific payment. + example: "Fn34o8g239v3wrb3t" + code: + type: string + description: Code received via SMS to validate and authorize a specific payment, only needed when business case requires it. Sending of this code is outside this specification. + example: "352673" + BodyAmountReservationTransactionForReserve: + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountReservationTransactionForReserve" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + validationInfo: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - description: Information to perform otp validation. Only needed when business case requires it. Sending of OTP is outside the scope of this specification. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + BodyAmountReservationTransactionForReserveInput: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: "#/components/schemas/AmountReservationTransactionForReserveInput" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + AmountReservationTransactionForReserve: + required: + - phoneNumber + - paymentAmount + - referenceCode + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: Uniquely identifies this payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. Same value as indicated in the request. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForReserve" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. Same value as the one provided in the request. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + example: "urn:payments:AK234rfweSBuWGFUEWFGWEVWRV" + serverReferenceCode: + type: string + description: + Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + example: "ref-pay-834tfr2rA3v8r8vr3rv-serv" + AmountReservationTransactionForReserveInput: + type: object + required: + - paymentAmount + - referenceCode + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForReserve" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + PaymentAmountForReserve: + type: object + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + paymentDetails: + $ref: "#/components/schemas/PaymentDetails" + PaymentDetails: + type: array + description: Detailed description of the concepts/items considered within a specific payment procedure. + minItems: 1 + items: + $ref: "#/components/schemas/PaymentItem" + PaymentItem: + type: object + required: + - id + - amount + - currency + - description + properties: + id: + type: string + description: |- + Unique payment item identifier. Relevant to uniquely identify an item within a given payment when `paymentDetails` are provided and also to correlate information when a refund regarding this item is performed, by means of using `refundDetails`. + example: "3goug3uvu32v3b" + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Specific amount to be charged or reserved referred to a specific item. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text referred to a specific item. + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount charged by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingInformation: + type: object + required: + - amount + - currency + - description + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Amount to be charged or reserved. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount charged by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingMetaData: + type: object + properties: + merchantName: + type: string + description: Indicates the merchant name. Allows aggregators/partners to specify the actual merchant name + example: "EA Sports" + merchantIdentifier: + type: string + description: Indicates the merchant identifier. Allows aggregators/partners to specify the actual merchant identifier + example: "eas-12345" + fee: + type: number + format: float + multipleOf: 0.01 + description: Percentage of the amount to be received by the requester + example: 10 + purchaseCategoryCode: + type: string + description: A category defining the type of service, product or media being purchased + example: "games" + channel: + type: string + description: The channel over which the requester is interacting with the merchant (e.g. WAP, Web, SMS...) + example: "web" + serviceId: + type: string + description: The identifier of the partner/merchant service being purchased + example: "games-online" + productId: + type: string + description: The product identifier to be combined with the `serviceId` to uniquely identify the product being purchased. For example if the `serviceId` relates to a VOD service, the `productId` can specify the movie rented + example: "138235321" + ValidationInfo: + type: object + required: + - action + properties: + action: + type: string + enum: + - open + - validate + description: Action to be done regarding otp validation. + discriminator: + propertyName: action + mapping: + open: "#/components/schemas/Open" + validate: "#/components/schemas/Validate" + example: + action: validate + authorizationId: "Fn34o8g239v3wrb3t" + Open: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - type: object + description: Information for otp validation by means of browseable URL. + required: + - validationURL + properties: + validationURL: + type: string + description: Backend generated Public URL to perform otp validation. Sending of OTP is outside the scope of this specification. + example: "https://my-payment-service.com/validate/358y24t2g4f2397g45" + Validate: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - type: object + description: Information for otp validation by means of received otp. + required: + - authorizationId + properties: + authorizationId: + type: string + description: Unique authorization identifier for a given payment to perform otp validation. Sending of OTP is outside the scope of this specification. Validation of this `authorizationId` is performed by means of `validatePayment` endpoint. + example: "Fn34o8g239v3wrb3t" + CloudEvent: + description: The notification format + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + minLength: 1 + example: "sd5e-uy52-88t4-za66" + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: Type of event as defined in each CAMARA API + minLength: 25 + example: "org.camaraproject.carrier-billing.v0.payment-reserved" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + minLength: 3 + example: "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: "application/json" + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.carrier-billing.v0.payment-pending-validation: "#/components/schemas/EventPaymentPendingValidation" + org.camaraproject.carrier-billing.v0.payment-reserved: "#/components/schemas/EventPaymentReserved" + org.camaraproject.carrier-billing.v0.payment-completed: "#/components/schemas/EventPaymentCompleted" + org.camaraproject.carrier-billing.v0.payment-cancelled: "#/components/schemas/EventPaymentCancelled" + org.camaraproject.carrier-billing.v0.payment-denied: "#/components/schemas/EventPaymentDenied" + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + DateTime: + type: string + format: date-time + description: Timestamp when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-11-03T12:27:10Z" + EventPaymentPendingValidation: + description: Event structure for payment pending validation + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentPendingValidation" + EventPaymentReserved: + description: Event structure for payment reserved + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentReserved" + EventPaymentCompleted: + description: Event structure for payment completed + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentCompleted" + EventPaymentCancelled: + description: Event structure for payment cancelled + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentCancelled" + EventPaymentDenied: + description: Event structure for payment denied + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentDenied" + PaymentPendingValidation: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-pending-validation event + - $ref: "#/components/schemas/BasicEvent" + PaymentReserved: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-reserved event + - $ref: "#/components/schemas/BasicEvent" + PaymentCompleted: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-completed event + - $ref: "#/components/schemas/BasicEvent" + - type: object + required: + - paymentDate + properties: + paymentDate: + type: string + description: Date when the payment is effectively performed, both in 1-step and 2-step scenarios. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + example: "2023-11-03T12:27:08.312Z" + PaymentCancelled: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-cancelled event + - $ref: "#/components/schemas/BasicEvent" + PaymentDenied: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-denied event + - $ref: "#/components/schemas/BasicEvent" + - type: object + properties: + denialReason: + type: string + description: Indicates the business reason for denying the payment. + example: "User is blocked due to pending debt" + BasicEvent: + type: object + description: Data type to provide basic payment event information + required: + - paymentId + - status + - description + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + status: + type: string + enum: + - succeeded + - failed + description: |- + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + example: "Payment Notification" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GetPaymentsInvalid400: + description: |- + Invalid input. In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Inconsistent paymentCreationDate.gte and paymentCreationDate.lte values ("code": "CARRIER_BILLING.INVALID_DATE_RANGE","message": "Client specified an invalid date range"). + - Request out of range ("code": "OUT_OF_RANGE","message": "Client specified an invalid range"). + - Too many matching records found ("code": "CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS","message": "Too many matching records found. Specify additional/suitable criteria to limit the number of records."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - CARRIER_BILLING.INVALID_DATE_RANGE + - CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_DATE_RANGE: + summary: Generic Invalid Date Range + description: Inconsistent paymentCreationDate.gte and paymentCreationDate.lte values + value: + status: 400 + code: CARRIER_BILLING.INVALID_DATE_RANGE + message: "Client specified an invalid date range." + GENERIC_400_OUT_OF_RANGE: + summary: Generic Out Of Range + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_TOO_MANY_MATCHING_RECORDS: + summary: Generic Too Many Matching Records + description: Too many matching records found + value: + status: 400 + code: CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS + message: "Too many matching records found. Specify additional/suitable criteria to limit the number of records." + PaymentInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - Currency is unknown or not authorized ("code": "INVALID_ARGUMENT","message": "Currency is unknown or not authorized"). + - clientCorrelator still exist ("code": "INVALID_ARGUMENT","message": "clientCorrelator already exist on server"). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_WRONG_CURRENCY: + summary: Generic Wrong Currency + description: Currency is unknown or not authorized + value: + code: INVALID_ARGUMENT + status: 400 + message: "Currency is unknown or not authorized." + GENERIC_400_DUPLICATE_CLIENT_CORRELATOR: + summary: Generic Duplicate Client Correlator + description: clientCorrelator still exist + value: + code: INVALID_ARGUMENT + status: 400 + message: "clientCorrelator already exist on server." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Payment2StepPrepareInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - paymentId is required ("code": "INVALID_ARGUMENT","message": "Expected property is missing: paymentId."). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_PAYMENT_ID_REQUIRED: + summary: Generic PaymentId required + description: paymentId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: paymentId." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Payment2StepInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - paymentId is required ("code": "INVALID_ARGUMENT","message": "Expected property is missing: paymentId."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_PAYMENT_ID_REQUIRED: + summary: Generic PaymentId required + description: paymentId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: paymentId." + ValidatePaymentInvalid400: + description: |- + Invalid input. + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - authorizationId is not valid ("code": "CARRIER_BILLING.INVALID_AUTHORIZATION_ID","message": "Invalid authorizationId."). + - code is not valid ("code": "CARRIER_BILLING.INVALID_CODE","message": "Invalid code."). + - validation failed ("code": "CARRIER_BILLING.VALIDATION_FAILED","message": "the maximum number of attempts have been consumed for this validation."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - CARRIER_BILLING.INVALID_AUTHORIZATION_ID + - CARRIER_BILLING.INVALID_CODE + - CARRIER_BILLING.VALIDATION_FAILED + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_AUTHORIZATION_ID_REQUIRED: + summary: Generic AuthorizationId Required + description: authorizationId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: authorizationId." + GENERIC_400_CODE_REQUIRED: + summary: Generic Code Required + description: code is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: code." + GENERIC_400_INVALID_AUTHORIZATION_ID: + summary: Generic Invalid Authorization Id + description: authorizationId is not valid + value: + code: CARRIER_BILLING.INVALID_AUTHORIZATION_ID + status: 400 + message: "Invalid authorizationId." + GENERIC_400_INVALID_CODE: + summary: Generic Invalid Code + description: code is not valid + value: + code: CARRIER_BILLING.INVALID_CODE + status: 400 + message: "Invalid code." + GENERIC_400_VALIDATION_FAILED: + summary: Generic Validation Failed + description: validation failed + value: + code: CARRIER_BILLING.VALIDATION_FAILED + status: 400 + message: "the maximum number of attempts have been consumed for this validation." + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + PaymentPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Payment denied by business ("code": "CARRIER_BILLING.PAYMENT_DENIED","message": "Payment denied by business."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING.PAYMENT_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_PAYMENT_DENIED: + summary: Generic Payment Denied + description: Payment denied by business + value: + status: 403 + code: CARRIER_BILLING.PAYMENT_DENIED + message: "Payment denied by business." + PaymentConfirmPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Payment denied by business ("code": "CARRIER_BILLING.PAYMENT_DENIED","message": "Payment denied by business."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING.PAYMENT_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_PAYMENT_DENIED: + summary: Generic Payment Denied + description: Payment denied by business + value: + status: 403 + code: CARRIER_BILLING.PAYMENT_DENIED + message: "Payment denied by business." + PaymentCancelPermissionDenied403: + description: |- + Client does not have sufficient permission. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + IdentifierNotFound404: + description: Phone Number Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Identifier2StepNotFound404: + description: |- + Resource Not Found. + In addition to regular NOT_FOUND scenario other scenarios may exist: + - Phone Number not found ("code": "IDENTIFIER_NOT_FOUND","message": "phoneNumber not found."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + PaymentConfirmConflict409: + description: |- + Conflict. In addition of regular ALREADY_EXISTS scenario other scenarios may exist: + - paymentId is already confirmed ("code": "CARRIER_BILLING.PAYMENT_CONFIRMED","message": "Payment has been confirmed."). + - paymentId is already cancelled ("code": "CARRIER_BILLING.PAYMENT_CANCELLED","message": "Payment has been cancelled."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + - CARRIER_BILLING.PAYMENT_CONFIRMED + - CARRIER_BILLING.PAYMENT_CANCELLED + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_ALREADY_CONFIRMED: + summary: Generic Already Confirmed + description: paymentId is already confirmed + value: + code: CARRIER_BILLING.PAYMENT_CONFIRMED + status: 409 + message: "Payment has been confirmed." + GENERIC_409_ALREADY_CANCELLED: + summary: Generic Already Cancelled + description: paymentId is already cancelled + value: + code: CARRIER_BILLING.PAYMENT_CANCELLED + status: 409 + message: "Payment has been cancelled." + PaymentCancelConflict409: + description: |- + Conflict. In addition of regular ALREADY_EXISTS scenario other scenarios may exist: + - paymentId is already confirmed ("code": "CARRIER_BILLING.PAYMENT_CONFIRMED","message": "Payment has been confirmed."). + - paymentId is already cancelled ("code": "CARRIER_BILLING.PAYMENT_CANCELLED","message": "Payment has been cancelled."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + - CARRIER_BILLING.PAYMENT_CONFIRMED + - CARRIER_BILLING.PAYMENT_CANCELLED + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_ALREADY_CONFIRMED: + summary: Generic Already Confirmed + description: paymentId is already confirmed + value: + code: CARRIER_BILLING.PAYMENT_CONFIRMED + status: 409 + message: "Payment has been confirmed." + GENERIC_409_ALREADY_CANCELLED: + summary: Generic Already Cancelled + description: paymentId is already cancelled + value: + code: CARRIER_BILLING.PAYMENT_CANCELLED + status: 409 + message: "Payment has been cancelled." + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + summary: Generic Gone + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + PaymentUnprocessable422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios that may exist: + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + - Unauthorized amount requested ("code": "CARRIER_BILLING.UNAUTHORIZED_AMOUNT","message": "Unauthorized amount requested."). + - Accumulated threshold amount for the user's mobile account overpassed ("code": "CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED","message": "Unauthorized payment request. Accumulated user mobile payments overpass account amount threshold."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - CARRIER_BILLING.UNAUTHORIZED_AMOUNT + - CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + GENERIC_422_UNAUTHORIZED_AMOUNT: + summary: Generic Unauthorized Amount + description: Unauthorized amount requested + value: + status: 422 + code: CARRIER_BILLING.UNAUTHORIZED_AMOUNT + message: "Unauthorized amount requested." + GENERIC_422_USER_MOBILE_ACCUMULATED_THRESHOLD_AMOUNT_OVERPASSED: + summary: Generic User Mobile Accumulated threshold Amount Overpassed + description: Accumulated threshold amount for the user's mobile account overpassed + value: + status: 422 + code: CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED + message: "Unauthorized payment request. Accumulated user mobile payments overpass account amount threshold." + PaymentSecondStepUnprocessable422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios that may exist: + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + summary: Generic Too Many Requests + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + default: 1 + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + default: 10 + StartPaymentCreationDate: + description: Initial `paymentCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: paymentCreationDate.gte + required: false + schema: + format: date-time + type: string + EndPaymentCreationDate: + description: End `paymentCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: paymentCreationDate.lte + required: false + schema: + format: date-time + type: string + Order: + description: Used to return the sorted results in descending (default) or ascending order, based on `paymentCreationDate` property + in: query + name: order + required: false + schema: + default: desc + enum: + - desc + - asc + type: string + PaymentStatus: + description: List of payment status to be considered for the query + in: query + name: paymentStatus + required: false + schema: + type: array + items: + type: string + enum: + - processing + - pending_validation + - denied + - reserved + - succeeded + - cancelled + MerchantIdentifier: + description: Merchant identifier to filter the results + in: query + name: merchantIdentifier + required: false + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer +``` diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cdf4cbeb08981c223cba66e9f8da28eb630d6fec --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap/raw.md @@ -0,0 +1,14 @@ +# Carrier Billing API roadmap + +**Phase 1 Features - Initial Version** +* Individual Payments Procedure +* Retrieve Details of a Payment Procedure +* OTP Payment validation (2FA SMS OTP) +* (Highly desired) 1-step / 2-step working mode +* (Highly desired) List of Payments Details per Service Provider and Customer (finding a solution to show only the payments performed by such an Service Provider) + +**Phase 2 Features - Future Versions** +* Support for Notifications +* Recurring Payments Procedure +* Refund Payments Procedure +* Features like 3DS secure banking diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..70db36400b68cfb3f7da6175defe78c418207770 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API/raw.md @@ -0,0 +1,251 @@ +# Overview + +The Carrier Billing Payment API provides programmable interface for developers and other users (capabilities consumers) to charge + a digital content purchase or subscription to the mobile line invoice. + +## 1\. Introduction + + +The Carrier Billing Payment API is used by an application to charge an amount on the +mobile line. It can be easily integrated and used through this secured API and +allows end-users to buy digital content in an easy & secured way. The API provides management of a payment entity and its associated lifecycle. + +The carrier billing Payment API is driven from Open Mobile Alliance standard. + + +## 2\. Quick Start + +The usage of the API is based on Payment resource, which can be created (in 1 or 2 steps process), confirmed (for 2-steps process), cancelled (for 2-steps process), queried and retrieved. + + +Before starting to use the API, the developer needs to know about the below specified details: + +**Payment service endpoint** +The URL pointing to the RESTful resource of the payment API. +As we manage 1-step and 2-steps process we have defined 2 separate tags to explicitly +distinct them in the swagger. A third tag 'payment' is defined for common operation for +both process (query & retrieve) + +**Authentication** +Security access keys such as OAuth 2.0 client credentials used by Client applications to invoke the Carrier Billing Payment API. + +**1-Step & 2-Steps** +1-Step process is very simple: The request intent is to charge an amount to the mobile line. When the server receives the request, it will check the user account associated with this line, and, if nothing prevents it, the amount is charged and will be either bill in next invoice or removed from current line credit. + +For 2-steps, the first call is to request a payment preparation. The amount is not charged and the server has to be ready to get a confirmation or a cancellation to perform the payment. Only when the confirmation is done, payment is charged. Depending on business rules of the Telco operator, a 'prepared' payment could expire after a defined delay. + +**Identifier for the mobile line to be charged** +To identify the mobile line to be charged an identifier **must** be provided. This identifier is mapped to the endUserId attribute. + + +**Notification URL** +Developers may provide a callback URL on which status change notifications, regarding the payment, can be received from the service provider. This is an optional parameter. + + + +Sample API invocations are presented in Section 4.6. + +## 3\. Authentication and Authorization + +The Carrier Billing Payment API makes use of the OAUTH 2.0 client credentials grant which is applicable for server to server use cases involving trusted partners +or clients without any protected user data involved. +In this method the API invoker client is registered as a confidential client with an authorization grant type of client_credentials [[1]](#1). + +## 4\. API Documentation + +### 4.1 API Version + +0.7.0 + +### 4.2 Details + +#### 4.2.1 API sequencing + +As described above, the API accommodates 2 distinct processes: one step process (direct request to charge) and two steps process (which requires an intermediate step to confirm/cancel a payment request) + +Following diagram shows the API resources operation sequencing + +
      + +PaymentSequence + +#### 4.2.1 API attributes + + +Attribute definition + +**Payment Class description:** + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| endUserId | Identify the mobile account to be charged - in general mobile number is provided | Mandatory attribute in POST request | +| clientCorrelator | Provided by the requester - Uniquely identifies this create charge request | Optionally valued by requester | +| paymentAmount | See PaymentAmount class table description| Mandatory attribute in POST request | +| referenceCode | Merchant generated payment reference to uniquely identify the request, for example the purchase or order identifier | Mandatory attribute in POST request | +| transactionOperationStatus | Specifies the payment status (example: Processing, Denied, Reserved, Succeeded, Cancelled) | Must be valued by server side (not in POST request) | +| resourceURL | URI of the created resource (same as in the Location header) | Only valued (optionally) by server side (not in POST request) | +| serverReferenceCode | Reference to the charge or refund, provided by the server, and meaningful to the server’s backend system for the purpose of reconciliation | Only valued (optionally) by server side (not in POST request) | +| paymentCreationDate | Date when the payment is created in server data base. This is a technically information | Only valued (optionally) by server side (not in POST request) | +| paymentDate | Date when the payment is effectively performed. This is a business information. | Only valued (optionally) by server side (not in POST request) | +| notificationUrl | Allows asynchronous delivery of purchase related events | Optionally valued by requester - if used, customer needs to have a notification endpoint | +| notificationAuthToken | Authentification token for callback API (if provided) | Optionally valued by requester | + +**PaymentAccount class description:** + +2 classes are defined: + +ChargingInformation: + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| amount | Amount to be charged or reserved (number) | Mandatory attribute in POST request | +| currency | Currency identifier as defined in [ISO4217] | Mandatory attribute in POST request | +| description | Description text to be used for information and billing text | Mandatory attribute in POST request| + + +ChargingMetaData + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| onBehalfOf | Allows aggregators/partners to specify the actual payee | Optionally valued by requester | +| purchaseCategoryCode | Allows aggregators/partners to specify the actual payee | Optionally valued by requester | +| channel | Channel where the order occurred | Optionally valued by requester | +| isTaxIncluded | if true, the amount is tax included, if false the amount is provided without tax. In both case, taxAmount could be valued to provide tax amount.| Optionally valued by requester | +| taxAmount | The tax amount charged by the merchant if the charge has tax already included (number). This also provides an indicator to the downstream billing system | Optionally valued by requester | +| serviceId | Identifier of service related to the payment | Optionally valued by requester | +| productId | Identifier of product related to the payment | Optionally valued by requester | + +**Payment State engine** + +Follow schema provides information about the payment state engine (state description & transition) + +PaymentState + + +### 4.3 Endpoint Definitions + +Following table defines API endpoints of exposed REST based for Carrier Billing Payment API management operations. + +| **Endpoint** | **Operation** | **Description** | +| -------- | --------- | ----------- | +| POST
      \/payment/v0/payments | **Create one step payment** | Create request for one step payment | +| POST
      \/payment/v0/payments/prepare | **Create two steps payment** | Create request for two steps payment | +| POST
      \/payment/v0/payments/{paymentId}/confirm | **Confirm a two steps payment** | Confirmation request for a prepared payment | +| POST
      \/payment/v0/payments/{paymentId}/cancel | **Cancel a two steps payment** | Cancellation request for a prepared payment | +| GET
      \/payment/v0/payments | **Query for payment** | Querying for payment(s) with criteria | +| GET
      \/payment/v0/payments/{paymentId} | **Retrieve payment** | Retrieve payment | +
      + +#### Carrier Billing Payment Resource Operations: +
      + +| **Create payment resource (one step)** | +| -------------------------- | +| **HTTP Request**
      POST \/payment/v0/payments
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      endUserId must be provided
      **Request Body Parameters**
      See above table for attribute definition.
      Following attributes are mandatory in the request: endUserId; paymentAmount.chargingInformation.amount; paymentAmount.chargingInformation.currency ; paymentAmount.chargingInformation.description ; referenceCode.
      Following attributes are only valued on server side and not present in POST request: transactionOperationStatus; resourceURL ; serverReferenceCode. + +
      **Response**
      **201: payment created**
      Response body: A complete payment representation as described in above table is provided.
      **400:** **Invalid input.**
      **401:** **Un-authorized.
      **403:** Forbidden.**
      **409:** **Conflict.**
      **500:** **Server Error.**
      **503:** **Service temporarily unavailable.** +
      + + +| **Create payment resource (two steps)** | +| -------------------------- | + **HTTP Request**
      POST \/payment/v0/payments/prepare
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      endUserId must be provided
      **Request Body Parameters**
      See above table for attribute definition. Following attributes are mandatory in the request: endUserId; paymentAmount.chargingInformation.amount; paymentAmount.chargingInformation.currency ; paymentAmount.chargingInformation.description ; referenceCode. Folowing attributes are only valued on server side and not present in POST request: transactionOperationStatus; resourceURL ; serverReferenceCode. + + **Response**
      **201: payment created**
      Response body: A complete payment representation as described in above table is provided.
      **400:** **Invalid input.**
      **401:** **Un-authorized.
      **403:** Forbidden.**
      **409:** **Conflict.**
      **500:** **Server Error.**
      **503:** **Service temporarily unavailable.** +
      + + +| **Confirm payment task (only for two steps process)** | +| -------------------------- | +**HTTP Request**
      POST \/payment/v0/payments/confirm/{paymentId
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      PaymentId must be provided
      **Request Body Parameters**
      endUserId must be provided + + **Response**
      **200: payment confirmation accepted**
      Response body: None

      **400:** **Invalid input.**
      **401:** **Un-authorized.
      **403:** Forbidden.**
      **409:** **Conflict.**
      **500:** **Server Error.**
      **503:** **Service temporarily unavailable.** +
      + +| **Cancel payment task (only for two steps process)** | +| -------------------------- | + **HTTP Request**
      POST \/payment/v0/payments/cancel/{paymentId}
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      endUserId and PaymentId must be provided
      **Request Body Parameters**
      endUserId must be provided + + **Response**
      **202: payment cancellation accepted**
      Response body: None

      **400:** **Invalid input.**
      **401:** **Un-authorized.
      **403:** Forbidden.**
      **409:** **Conflict.**
      **500:** **Server Error.**
      **503:** **Service temporarily unavailable.** +
      + + +#### Query for payment resource + +| **Quering payment Resource /id information** | +| --------------------------------------- | +| **HTTP Request**
      GET\/payment/v0/payments/{paymentId}
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      paymentId: paymentId id that was obtained from the Create payment operation.
      **Request Body Parameters**
      No request body parameters are defined.
      **Response**

      **200: Payment information returned.**
      Response body:
      Complete payment representation as defined in the above table.

      **401:** Un-authorized.
      **403:** Forbidden.
      **404:** Payment not found.
      **503:** Service temporarily unavailable. | +
      + + +| **Quering payment Resource /list information** | +| --------------------------------------- | +| **HTTP Request**
      GET\/payment/v0/payments/{paymentId}
      **Query Parameters**
      No query parameters are defined.
      **Path Parameters**
      endUserId: Identify the mobile account charged - in general mobile number is provided
      fields: Comma-separated attributes to be provided in response
      offset: Requested index for start of resources to be provided in response
      limit: Requested number of resources to be provided in response
      **Request Body Parameters**
      No request body parameters are defined.
      **Response**

      **200: a list of payment(s).**
      Response body:
      An array of payment representation (could be a subset of a complete representation depending on fields filtering).
      Note: It could be empty list if no payment match search criteria.

      **401:** Un-authorized.
      **403:** Forbidden.

      **503:** Service temporarily unavailable. | +
      + +### 4.4 Errors + +Since CAMARA Carrier Billing Payment API is based on REST design principles and blueprints, well defined HTTP status codes and families specified by community are followed [[2]](#2). + +Details of HTTP based error/exception codes for the Carrier Billing Payment API are described in Section 4.3 of each API REST based method. +Following table provides an overview of common error names, codes, and messages applicable to Carrier Billing Payment API. + +| No | Error Name | Error Code | Error Message | +| --- | ---------- | ---------- | ------------- | +|1 |400 | INVALID_INPUT | "Expected property is missing: endUserId" | +|2 |400 | INVALID_INPUT | "Expected property is missing: referenceCode" | +|3 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.amount" | +|4 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.currency" | +|5 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.description" | +|6 |400 | INVALID_INPUT | "Expected property is missing: paymentId" | +|7 |400 | INVALID_INPUT | "Expected property is missing: qos" | +|8 |400 | INVALID_INPUT | "Payment status does not allow to confirm it" | +|9 |400 | INVALID_INPUT | "Payment status does not allow to cancel it" | +|10 |401 | UNAUTHORIZED | "No authorization to invoke operation" | +|11 |403 | FORBIDDEN | "Operation not allowed" | +|12 |404 | NOT_FOUND | "Payment Id does not exist" | +|13 |409 | CONFLICT | "Another payment is created for the same client correlator" | +|14 |500 | INTERNAL | "Payment could not be created" | +|15 |503 | SERVICE_UNAVAILABLE | "Service unavailable" | + +### 4.5 Policies + +N/A + +### 4.6 Code Snippets +
      +Snippet 1, elaborates REST based API call with "*curl"* to create a payment for a Video on demand payment + + + +Please note, the credentials for API authentication purposes need to be adjusted based on target security system configuration. + +| Snippet 1. Create Payment resource | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/payment/v0/payments`
      -H 'accept: application/json'
      -H 'Content-Type: application/json'
      -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
      -d '{
      "amountTransaction": {
      "endUserId": "+33068741256+d",
      "paymentAmount": { "chargingInformation": { "amount": 2.99, "currency": "EUR", "description": "VOD charge" },
      "chargingMetaData": {
      "onBehalfOf":"VOD Service",
      "purchaseCategoryCode": "Purchase Movie",
      "channel": "TV",
      "taxAmount": 0.84,
      "isTaxIncluded": true,
      "serviceId": "N/A",
      "productId": "vod-47" }
      },
      "referenceCode": "vod081220225698",
      "clientCorrelator": "78g9-dfg6-fgtr6" },
      "notificationUrl": "https://callback..." | +| response will be:
      201
      -d '{
      "amountTransaction": {
      "endUserId": "+33068741256+d",
      "paymentAmount": { "chargingInformation": { "amount": 2.99, "currency": "EUR", "description": "VOD charge" },
      "chargingMetaData": {
      "onBehalfOf":"VOD Service",
      "purchaseCategoryCode": "Purchase Movie",
      "channel": "TV",
      "taxAmount": 0.84,
      "isTaxIncluded": true,
      "serviceId": "N/A",
      "productId": "vod-47" }
      },
      "referenceCode": "vod081220225698",
      "clientCorrelator": "78g9-dfg6-fgtr6",
      "transactionOperationStatus": "succeeded",
      "resourceURL": "https://localhost:9091/payment/v0/payments/7896321",
      "serverReferenceCode": "7896321" },
      "paymentCreationDate" : "2023-03-10T15:30:58.139Z",
      "paymentDate" : "2023-03-10T15:31:04.139Z",
      "notificationUrl": "https://callback..." }'| +
      + + +### 4.7 FAQ's + +(FAQs will be added in a later version of the documentation) + +### 4.8 Terms + +N/A + +### 4.9 Release Notes + +0.6 Release note +* Added status attribute in Error +* Added attribute notificationAuthToken + +0.7 Release note +* Added paymentCreationDate & PaymentDate +* Added isTaxIncluded flag +## References + + +[1] [CAMARA Commonalities : Authentication and Authorization Concept for Service APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Working/CAMARA-AuthN-AuthZ-Concept.md)
      +
      [2] [HTTP Status codes spec](https://restfulapi.net/http-status-codes/)
      diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9d74979d0434803c83d3c14493c8920445a37983 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Carrier Billing v0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Carrier Billing User Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/_oDWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b32f4d7f6ee0a49dca9a3dc33a5dc2bd9148b547 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story/raw.md @@ -0,0 +1,52 @@ +**User Story: Make a Payment request in one step** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment (one-time fee -in initial phase- or recurring -in a later phase- ) to be billed against a customer's carrier bill, so that I can offer customers payment alternatives. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Payment on Carrier Bill* \- Initiate Carrier Billing approval process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has Carrier Billing activated as payment method.
      2. The Customer:User has initiated payment via Carrier Billing from application/portal/product channel
      3. The PaymentRequester has verified that associated carrier billing service belongs to the Customer:User (Generally as part of adding a new payment method, 2-Factor-Authorization or equivalent)
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to trigger the payment.
      **Ends when:** The payment is completed and the customer application customer can query details of that payment.
      | +| ***Post-conditions*** | After customer application server performs the payment, payment details can be queried. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Invalid input: Not valid input data to invoke operation (e.g. merchant information not provided or unknown).
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the payment
      • Conflict: Internal configuration policies don't allow for Payment Execution/Cancellation.
      | + + +**User Story: Make a Payment request in two steps** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment (one-time fee -in initial phase- or recurring -in a later phase- ) to be billed against a customer's carrier bill, so that I can offer customers payment alternatives. The payment process will be split in 2 parts:
      1. Payment preparation request (that did not trigger the payment but only prepare it)
      2. Payment confirmation or cancellation. The payment confirmation triggers the payment itself. Optionally, as per business needs, payment confirmation may require a payment validation in advance (i.e. an optional step between payment preparation and payment confirmation)
      | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Payment on Carrier Bill* \- Initiate Carrier Billing 2-steps approval process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has Carrier Billing activated as payment method.
      2. The Customer:User has initiated 2-steps payment via Carrier Billing from application/portal/product channel
      3. The PaymentRequester has verified that associated carrier service belongs to the Customer:User (Generally as part of adding a new payment method, 2FA or equivalent)
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to trigger a 2-steps payment.
      **Intermediate steps:** The customer application server makes a request to confirm or cancel the payment preparation
      **Ends when:** If payment confirmation is provided the payment is completed. If a payment cancellation is provided (explicit cancellation) or if neither a confirmation or cancellation is received after a predefined business delay (implicitly by expiration), the payment preparation is cancelled.
      For both cases the customer application can retrieve and/or query details of that payment
      | +| ***Post-conditions*** | After customer application server performs the payment, payment details can be queried. A payment can stay in preparation status only for a predefined business delay. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Invalid input: Not valid input data to invoke operation like for example:
        merchant information not provided or unknown,
        payment identifier not existing or not linked to the customer:user,
        payment confirmation for an expired payment,
        payment cancellation request for an already confirmed payment).
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the payment. Payment preparation as payment confirmation could be denied
      • Conflict: Internal configuration policies don't allow for Payment Execution/Cancellation.
      | + + +**User Story: Retrieve a Payment from its identifier** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get details of one performed payment (from its id) by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Payments Details done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has performed payments via application, both success and failed
      2. The Customer:User has payment identification.
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to get payments details performed via that application providing payment identifier.
      **Ends when:** Response is received from Carrier Billing service showing the payment details | +| ***Post-conditions*** | Requester receives a complete representation of the payment. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Invalid input: Not valid payment identifier to invoke operation.
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the payment
      | + + +**User Story: Retrieve a Payment list** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get a list of performed payments from criteria (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Payments list done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has performed payments via application, both success and failed
      2. The requester provides a list of criteria(s) to select payment (Customer/user identifier, payment status)
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to get payment/payments details performed via that application
      **Ends when:** Response is received from Carrier Billing service showing the details | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the payment
      | + +
      diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..010281ad1d014919a9f32cdb97070a66043075c5 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Carrier Billing Refund v0.3.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing-refund.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing-refund.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Carrier Billing Refund User Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYBSBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story/raw.md b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eb4d8effc70746052dd963a08ccbd650c726b5b1 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story/raw.md @@ -0,0 +1,52 @@ +**User Story: Make a Payment Refund request in one step** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment refund (_total_: requesting whole payment amount or whole remaining payment amount not yet refunded, so as no more refunds can be requested; or _partial_: requesting a specific payment amount refund less than the overall amount related to the payment done, so as in principle more refunds can be requested, until performing a total refund or not having remaining payment amount to be refunded) to be billed against a customer's carrier bill. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Refund on Carrier Bill* \- Initiate Carrier Billing Refund process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has Carrier Billing activated as payment method.
      2. The Customer:User has initiated Refund via Carrier Billing from application/portal/product channel
      3. The RefundRequester has verified that associated carrier billing service belongs to the Customer:User (Generally as part of adding a new payment method, 2-Factor-Authorization or equivalent)
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to trigger the refund.
      **Ends when:** The refund is completed and the customer application customer can query details of that refund.
      | +| ***Post-conditions*** | After customer application server performs the refund, refund details can be queried. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Invalid input: Not valid input data to invoke operation (e.g. invalid paymentId).
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the refund
      • Conflict: Internal configuration policies don't allow for Refund Execution.
      | + + +**User Story: Retrieve a Payment Refund from its identifier** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get details of one performed refund (from its id) by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Refund Details done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has performed refunds via application, both success and failed
      2. The Customer:User has payment identification and refund identification.
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get refund details performed via that application providing payment identifier and refund identifier.
      **Ends when:** Response is received from Carrier Billing Refund service showing the refund details | +| ***Post-conditions*** | Requester receives a complete representation of the refund. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Invalid input: Not valid payment identifier or refund identifier to invoke operation.
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the refund
      | + + +**User Story: Retrieve a Payment Refunds list** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get a list of performed refunds, for a given payment, from criteria (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Refunds list done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has performed refunds via application, both success and failed
      2. The requester provides a list of criteria(s) to select refund (Customer/user identifier, refund status)
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get refund/refunds details performed via that application
      **Ends when:** Response is received from Carrier Billing Refund service showing the details | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the refund
      | + + +**User Story: Retrieve a Payment Amount Not Refunded yet** +
      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get the remaining amount not yet refunded for a given payment (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
      **Actors:** Application service providers, hyperscalers, application developers.
      **Scope:** *Request Remaining Amount not yet refunded done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:User has performed refunds via application, both success and failed
      2. The requester provides payment identification
      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get the remaining amount not yet refunded for a given paymentId performed via that application
      **Ends when:** Response is received from Carrier Billing Refund service showing the remaining amount not yet refunded | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
      • Unauthorized: Not valid credentials (e.g. use of already expired access token). | + +
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..02bfe55909dcedf9fc0e06163550e2891444913b --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07/raw.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-jun-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Jan Friman (ERICSSON) +- Rittwik Jana (GOOGLE) +- Masaharu Hattori (KDDI) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG (ORA,TEF) | Decision in CAMARA API for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +New Participants | Welcome to Rittwik, Masa and Jim. Explained the current situation within the CAMARA Carrier Billing WG +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Telefonica introduces rationale and history behind the Issue. Current status is trying to reach an agreement and not wait for a vote that can be delayed in time.
        • Therefore, after internal checking, Telefonica is OK to consider Orange proposal under certain conditions. Points under consideration are listed in this [PowerPoint Slide](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/CarrierBilling_AgreementProposal_20230607.pptx).
        • Orange has initially agreed in these conditions.
        • Based on this initial agreement, Telefonica & Orange will work to integrate all these points in a common contribution. We are open to comment/issue from the team.
        • Good feedback from the team waiting to receive that common input (Ericsson, STC).
        • Google asks if there is currently an API for this WG. Orange indicates there is not yet, there are two proposals and Orange and Telefona are working on presenting a common proposal based on agreement guidelines.
        • Telefonica indicates hopefully to have an initial common proposal soon because wants to promote Carrier Billing API in an MVP this year. If needed, ad-hoc meeting can be scheduled to present&discuss proposal. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4f739a54022f9133708900b7e411568bf32dc182 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09/raw.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 09-nov-2022
        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Albaraa Bajnaid (STC) +- Pedro Díez (Telefonica) + +## Goals +Attendees presentation
        +Initial aligment on features
        +Initial point of view of participants + +Item | Who | Description +---- | ---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Telefonica | Initial API Proposal + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | Two User Stories defined, one related to Payment procedure and the other one related to Payment Method Provisioning/Onboarding. About the first one, there are no relevant comments and participants are aligned about it. Regarding the second one, STC comments about some business scenarios (Apple), in which payment method provisioning is needed. On this matter, Orange and Telefonica provide comments in the line that this functionality is not really part of "core" payment functionalty, so this functionality maybe fits in later version or other CAMARA track. +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | A first set of features are commented to check participants view on them:
        **Individual Purchase/Payment**:
        • Orange: Model is splitted and purchase and payment are 2 distinct entities (with of course relationship. They have their own lifecycle. From Orange perspective, priority is payment. Individual Payment is first priority.
        • STC: Individual Payment is also first priority.
        • Telefonica: Analogous comment, this feature is first priority
        **Recurrent Purchase/Payment (a.k.a. subscriptions)**: All participants agree on having this feature as a second priority
        **OTP Payment validation (2FA SMS OTP)**: All participants have the same view on considering this feature as first priority.
        • STC also indicates the need to deal with scenarios managed not only by SMS OTP but also via Push Notifications
        **Retrieve Purchase/Payment Details**: All participants agree on having payment details as a first priority feature. Also list of payments is commented as a valuable feature.
        • In baseline proposal not included the list feature by Telefonica due to the fact of managing payment list between different Apps (scenario: one App cannot see payments performed by other App and viceversa)
        **Refund**: All participants share the view of having this feature as a second priority
        NOTE: Orange indicates within this issue the consideration of having 1/2-STEP payment flow approach (i.e. having both options at OBs discretion). [Reference Flow](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/Carrier%20Billing%20sequence%20diagram.png) +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Initial API Proposal.
        • Telefonica introduces the initial proposal, indicating the concepts of Purchase and Payments, the 2-step process (prepare and confirm/cancel) and the asynchronous option behaviour -via notifications_uri-).
        Orange provides two comments over it:
        • Purchase / Payment model splitted (relationship between both concepts are done by reference: an order could refer a payment, then the comment about focusing on Payment withing this track).
        • Use of notifications seen technically as a good approach, however experience observed with end developers indicates more frequent the use of polling. So proposing to have notifications in a latter phase.
        • STC asks about OTP validation procedure, how it works. Telefonica indicates initially thinking in a process embbebed within Payment Preparation Phase (managed internally by OB systems, that generate an SMS towards authorized msisdn and provide info in response to present OTP validation link.
        As part of this issue discussion, Orange comments about having a view about payment status and available transactions between them. + +### Next Steps +- Agree on first proposal features scope @PedroDiez initiates issue +- Work on Payment status and transitions @PedroDiez initiates issue +- Think about options for OTP validation (in 1-STEP scenario as well in order to figure out) @all diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b3cb09bf9be30ce856b2dc096839c169862a55c5 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16/raw.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 16-nov-2022
        +**Status:** FINAL + +## Attendees +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Mohammed Nayeenuddin (STC) +- Mohammed Amir (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
        +Aligment on features - first phase
        +Inform about merging of initial draft in this week +Inform about having first stable API version by 28/30 Nov. + + +Item | Who | Description +---- | ---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Telefonica | Initial API Proposal + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | Agreed User Story defined related to Payment procedure. Pending Details to be completed. New one about Obtain Payment(s) Details should be added. +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Features grouping in phases talked in the meeting. Orange and Telefonica OK with that grouping. STC to provide feedback by tomorrow (17/11). +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Initial API Proposal.
        • Telefonica comments CAMARA Steerco guideline to have draft proposal by 18/11. Proposes to merge initial v0.1.0 with Disclaimer is draft proposal, because there are points to be still analyzed/discussed. Will wait for STC tomorrow feedback to make initial adjustments prior to merge
        • **Purchase/Payment**: Telefonica comments its proposal is to keep purchase concept and Orange comments do not see purchase concept in the model. So OPEN point for further discussion. Orange also indicates in the meeting it will provide a swagger contribution without purchase concept to help understanding of this different approach. Provided after the meeting in [Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16)
        • **1-step/2-step**: Up to OBs discretion, both would be allowed. 1-STEP: payment performed in 1 interaction (confirm-execute). 2-STEP: payment performed in 2 interactions (prepare/confirm-execute). CancelPayment procedure only applies in a 2-STEP model. [Reference Flow](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/Carrier%20Billing%20sequence%20diagram.png)
        • **otp_validation**: In 1-step, initially would fit into procedure response. In 2-step, it would apply in preparePayment response. Better to see in a flow.
        • **User identification**. Raised by STC in order to provide MSISDN. Telefonica explains Use Case is Mobile access so OB Mobile IP authentication features would identify MSISDN subscription. Then that can be associated (outside API scope) to Authorization issued, so MSISDN is not really required to be indicated. Orange shares STC concern about the issue 3 as they have scenario where the API requester could be another party and then a MSISDN or an end user id must be available in the request. +[Issue 15 - Carrier Billing Checkout Status](https://github.com/camaraproject/CarrierBillingCheckOut/issues/15) Explained during the meeting. To be checked by participants offline + +### Next Steps +- After the meeting closed informative issues: +[Issue 12 - Adding Diagram to show 1-STEP, 2-STEP Model] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/12) +[Issue 13 - MoM 09/NOV available](https://github.com/camaraproject/CarrierBillingCheckOut/issues/13) +- Check by participants offline Issue 15 documentation +- Improve User Stories. Add the one about Payment Details +- [Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) Update initial proposal for initial v0.1.0 draft merge after feedback by STC of issue 10. Also update diagrams diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c2ded7971005063b375fef1269c16f0465dccb7d --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23/raw.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 23-nov-2022
        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Udaka Kappagoda (Dialog Axiata) +- Ushan Kanahitiyanage (Dialog Axiata) +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Albaraa Bajnaid (STC) +- Mohammed Nayeenuddin (STC) +- Mohammed Amir (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
        +Review Orange's contribution + + +Item | Who | Description +---- | ---- | ---- +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16) | Orange | Orange Contribution for Carrier Billing + + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Based on that issue, a PR is generated. [Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18). Kind request to be reviewed by the WG team (some reviewers added) for approval, in order to be merged. Expected for this week. +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC updates PR during the week to gather first two scenarios. Kind request to be reviewed by the WG team for approval, in order to be merged. Expected for this week. +[Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16) | Orange explains its proposal for Carrier Billing. Before initiating explanation Telefonica comments about discussion thread in git:
        • Telefonica proposal do not include some cases (invoices) as no Use Case so far. Regarding differents payments (for items) for one purchase, in the same fashion. Orange clarifies just making some payments for the items included in a payment.

        Orange explains its proposal baseline: Proposal OMA-based, explaining they see a model following OMA body structures guidelines, maybe adding/removing some params to be aligned with Use Cases and provide a simpler interface as possible. Input structures for 1-STEP/2-STEP initiation procedures are analogous, provides initial explanation about semantic of params. Maybe responses could be simplified. Some comments around some params raised from STC (tax_amount, channel) and Telefonica (conceptualization of items in model). PurchaseId could be included as an addition of OMA-based input.
        Situation: This proposal has a different approach with regards to Telefonica one [Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3), whose baseline is [Pull Request 4](https://github.com/camaraproject/CarrierBillingCheckOut/pull/4). Orange sees Purchase/Payment as different business concepts whilst Telefonica considers Purchase as the object that models the concept to be paid and the payment the action of charging for it. Telefonica needs to check internally this approach in order to provide feedback and comment if it can be accepted. + + +### Next Steps +- After the meeting closed informative issues: +[Issue 17 - MoM 16/NOV available](https://github.com/camaraproject/CarrierBillingCheckOut/issues/17) +- Telefonica will comment about Orange proposal +- Next meeting 30/NOV diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b51d66a275417dfe8a00a6fcc411a820cf25c3cb --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01/raw.md @@ -0,0 +1,40 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 01-dec-2022
        +**Status:** FINAL + +## Attendees +- Vaishali Gupta (Dell Technologies) +- Gareth Williams (GSMA) +- Ludovic Robert (Orange) +- Nayeenuddin Mohammed (STC) +- Amir Mohammed (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
        +Inform about status in WG + + +Item | Who | Description +---- | ---- | ---- +[Issue 20](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | Telefonica | MoM 23/NOV +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | WG | Open Contributions to WG + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 20](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | MoM available in [Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19). Agreed but cannot be merged after activation of merging rules. Ludovic (Orange) kindly offers to be codeowner. Requested in [Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | PR content is agreed [Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18). Pending to be approved to be merged. +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | CLOSED. Agreed initial input from STC and merged after the meeting.
        • Orange proposes to generate 4 User Stories (User Stories for 1-STEP and 2-STEP procedures and User Stories for Retrieve Details of a Payment and List Payments based in some criteria).
        • Accepted in the meeting and Orange will make proposal +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | Opened to reflect current status of two different proposals presented by Telefonica and Orange that cannot be accepted each other. Commented in the meeting that this issue is open to provide free opinion from other participants about any preference. Tomorrow it will be a call to discuss about rules/procedures regading this type of situations. Waiting to have guidance to move forward. Some discussion around this:
        • STC asks about how to deal with OTP in proposal from Orange and the need of merchant information to be mandatory.
        • Orange comments that merchant information can be accomodated and regarding OTP validation they see as a separate functionality implemented via a MC-based solution.
        • Telefonica indicates in its proposal OTP validation is internally triggered as Backend Logic (generating SMS towards user) and API returns URL where OTP can be validated. + + +### Next Steps +- Approval of Pull Request 22 to deal with weekly activities within WG (needed at least two "operative" codeowners) +- Approval of Pull Requests 18 and 19 +- Next meeting 07/DEC diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..75c664a60af2cd8b8e6d58870adbf6d70d48036d --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07/raw.md @@ -0,0 +1,55 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-dec-2022
        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Ludovic Robert (Orange) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG
        +Inform about progress of Issues/PRs +Next Steps + + +Item | Who | Description +---- | ---- | ---- +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | WG | Open Contributions to WG +[Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) | WG | Adding Ludovic as codeowner +[Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18) | Telefonica | Roadmap Of features +[Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19) | Telefonica | MoM 23/NOV +[Pull Request 23](https://github.com/camaraproject/CarrierBillingCheckOut/pull/23) | Telefonica | MoM 23/NOV +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | Orange | User Story update + payment state engine +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | Orange | Carrier Billing Payment Proposal v0.5 +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | Telefonica | Carrier Billing Checkout Proposal v0.5 + + +### Items Discussion + +Item | Discussion +---- | ---- + +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | As per output of 02/DEC meeting, proposals from Orange and Telefonica will be part of Carrier Billing family APIs. Keep this issue opened to track alignment of relevant actions to fullfil documentation for both. Target to have APIs documentation is 16th December.
        +[Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) | New codeowner added (Ludovic), given acceptance from Markus. This will allow WG to progress in main work in the short term.
        +[Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18) | Roadmap of features. MERGED. CLOSED related Issue 10.
        +[Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19) | MoM 23/NOV. MERGED. CLOSED related Issue 20.
        +[Pull Request 23](https://github.com/camaraproject/CarrierBillingCheckOut/pull/23) | MoM 01/DEC. MERGED.
        +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | User Story update + payment state engine.
        • Orange explains the rationale of the proposal and the separation in 4 US. Additionaly, it provides a Payment state machine.
        • Telefonica understands Payment state model, same statuses although with some different names. Will review contribution offline
        • STC will review offline this contribution.
        ALL, review contribution and provide comments/give OK.
        +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | To be merged after meeting. If anyone has doubts/comments, it may be provided offline.
        +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | To be merged after meeting. If anyone has doubts/comments, it may be provided offline.
        + + +### Next Steps +- Documentation required: + - API readiness Checklist. Telefonica to update filename to remove "Checkout" + - User Stories. To have it completed Pull Request 25 is pending to be merged + - API Proposals yaml. Ongoing with Pull Requests 26 and 27 to be merged after the meeting + - Full API documentation. See next point +- Elaborate full documentation for both proposals (Orange/Telefonica). [Points](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-DocumentationTemplate.md) to be covered. [Example reference](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoD_API.md) +- APs: @PedroDiez + - Once APIs Proposals are merged, generate PR to remove old ones. + - Review and Update naming of some documents (removing wording checkout, as are common to APIs family) +- Next meeting 14/DEC diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4020fc36dd2578c896980be80c3ead137ebd144e --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14/raw.md @@ -0,0 +1,53 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 14-dec-2022
        +**Status:** FINAL + +## Attendees +- Ludovic Robert (Orange) +- Aamir Aftab Muhammad (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG
        +Inform about progress of Documentation/PRs +Next Steps + + +Item | Who | Description +---- | ---- | ---- +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | Orange | User Story update + payment state engine +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | Orange | Carrier Billing Payment Proposal v0.5 +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | Telefonica | Carrier Billing Checkout Proposal v0.5 +[Pull Request 28](https://github.com/camaraproject/CarrierBillingCheckOut/pull/28) | WG | MoM 07-DEC +[Pull Request 29](https://github.com/camaraproject/CarrierBillingCheckOut/pull/29) | Telefonica | Rename documentation files +[Pull Request 30](https://github.com/camaraproject/CarrierBillingCheckOut/pull/30) | Telefonica | Remove old files +[Pull Request 31](https://github.com/camaraproject/CarrierBillingCheckOut/pull/31) | Telefonica | User Stories format +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Orange | Carrier Billing Payment API documentation + Yaml update + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | CLOSED. Merged after meeting
        +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | CLOSED. Merged after meeting
        +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | CLOSED. Merged after meeting
        +[Pull Request 28](https://github.com/camaraproject/CarrierBillingCheckOut/pull/28) | WG | MoM 07-DEC. Pending approval
        +[Pull Request 29](https://github.com/camaraproject/CarrierBillingCheckOut/pull/29) | CLOSED. Merged during week. Rename some documentation files to take off "checkout" wording and be generic for Carrier Billing APIs family
        +[Pull Request 30](https://github.com/camaraproject/CarrierBillingCheckOut/pull/30) | CLOSED. Merged during week. Remove old contribution files for folder clean-up.
        +[Pull Request 31](https://github.com/camaraproject/CarrierBillingCheckOut/pull/31) | CLOSED. Merged during week. Fixing some format of the User Stories file.
        +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Carrier Billing Payment API documentation + Yaml update. API Documentation for Carrier Billing Payment Proposal.
        To be reviewed by Team. Telefonica comments it will provide its proposal documentation by 15/DEC.
        STC comments about how to manage OTP validation in this proposal. Orange indicates they see as a separate functionality that can be manged by other means. Also STC comments about consent management and Orange and Telefonica indicates that track is part of Commonalities WG. + + +### Next Steps +- Documentation required: + - Full API documentation. Target is 19/DEC + - On 15/DEC contributors completed/merged their proposals:
        + - Orange Contribution [Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) + - Orange - Minor Update in Payment State Engine Picture [Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) + - Telefonica Contribution [Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) + +- Next meeting 19/DEC. Short meeting. diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d07c76cd367c820999f5ad86e4cac9db9dc535a3 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21/raw.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-dec-2022
        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Aamir Aftab Muhammad (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG: Proposals yaml and documentation provided
        +Next Meetings schedule + +Item | Who | Description +---- | ---- | ---- +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Orange | Carrier Billing Payment API documentation + Yaml update +[Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) | Telefonica | Carrier Billing Checkout API documentation + Yaml update +[Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) | Orange | Update in Payment State Engine Picture + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Carrier Billing Payment API documentation + Yaml update. CLOSED. Merged on 18/DEC. +[Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) | Carrier Billing Checkout API documentation + Yaml update. CLOSED. Merged on 18/DEC +[Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) | Update in Payment State Engine Picture. CLOSED. Merged on 18/DEC +WG Status | Documentation and yaml of both proposals is available.
        • [APIs Documentation](https://github.com/camaraproject/CarrierBillingCheckOut/tree/main/documentation/API_documentation)
        • [YAMLs](https://github.com/camaraproject/CarrierBillingCheckOut/tree/main/code/API_definitions)
        Telefonica indicates if there is any comment regarding its proposal. STC comments that will review proposal offline and provide comments/doubts. +Meetings Schedule | Mainly talked offline with Orange and STC to move 16:00 GMT+1 next year. In principle keep weekly meetings during January/February and review later periodicity. + +### Next Steps +- Meetings schedule to be performed to begin at 16:00 Wednesdays next year (avoid collisions with Commonalities WG). @PedroDiez to generate issue and related PR. +- Next Meeting 18/JAN diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4b7749a3b23d1045be563979b88341d3ab538069 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18/raw.md @@ -0,0 +1,41 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 18-jan-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Gareth Williams (GSMA) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Planning next steps in WG
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange | Update readme.md file to indicate that 2 flavors are defined + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Documentation and yaml of both proposals available. Version v0.5. Brief summary explanation of the status of the working group for new participants to have some context about work carried so far +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange proposes to align Carrier Billing API error structure with regards to commonalities error model defined. It is agreed to do so as it was a pending action from last year.
        • This aligment will be done in v0.6.
        • Telefonica comments will also apply and from its side some fetaures are still pending to be included (notifications, 1-step payment, list of payments).Maybe notifications model will be included along with error aligment
        • v1.0 is targeted to have both proposals aligned with first set of functionalities.
        • Pull Requests to be generated by Orange and Telefonica +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Traversal track coming from Commonalities WG. Intention is to have a Glossary Terms information within CAMARA with relevant terms of each WG.
        Agreed to use the issue to compile relevant terms and definitions within WG (everyone can contribute) and once agreed Pedro will check with commonalities WG how to incorporate to the document (i.e trigger Pull Request) +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange proposes to add some explanation in README.md file of WG "root" folder about the existance of two flavours of APIs to facilitate the understanding of the situation within the WG.
        Agreed to do so and move forward. Orange will elaborate proposal and generate Pull Request +ERICSSON questions | Ericsson asks some questions about both proposals. Mainly to know the difference between them (mainly the separation of concepts of purchase and payment in Telefonica porposal) and understand the working behaviour. Lifecycle of both proposals is also explained.
        Regarding Telefonica proposal Ericsson asks about lifecycle of Purchases (how to manage Purchases that are never been tried to be payed). Telefonica will check how it manages it, although commented severals options may be implemented. Also about the use of fee, that will be internally checked. It also comments about possibility to provide order_id with another name. It is commented in the short/mid term it is not intended to be changed. +STC questions | STC comments will send offline some questions/doubts about Telefonica proposal + + +### Next Steps +- Next Meeting on 25th January diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..439320f9204b4eb6015a3068a8839c737f194220 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25/raw.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-jan-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues and Ongoing PRs
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange | Update readme.md file to indicate that 2 flavors are defined +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | Orange | Update README.md file - PR associated to [Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model + + +### Items Discussion + +Item | Discussion +---- | ---- +Management Topics | Ajit, Fahad and Nayeemuddin access to WG. Provided offline instructions after meeting to Ajit and Nayeemuddin to manage subscription to WG. Once subscription done and with Githug users, they should have access to WG documentation and discussion tracks. +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | PR associated to Issue 46.
        Reviewed by Telefonica, given approval. Minor comment after the meeting provided. @ALL to provide any additional comment until Monday 30th January EOD. +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange proposes to align Carrier Billing API error structure with regards to commonalities error model defined. It is agreed to do so as it was a pending action from last year.
        • This aligment will be done in v0.6.
        • Telefonica comments will also apply and from its side some features are still pending to be included (notifications, 1-step payment, list of payments).Maybe notifications model will be included along with error aligment
        • v1.0 is targeted to have both proposals aligned with first set of functionalities.
        • Pull Requests to be generated by Orange and Telefonica +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange contribution to deal with Issue 44 and Issue 47. Telefonica provides some comments and see proposal coherent in general. Discussion over it:
        • Agreed to do version update over same YAML (Telefonica to do the same on its contribution).
        • "status" pattern "^[4-5][0-9]{2}$". Commented it is a point to reflect in Commonalities. Telefonica indicates it will comment internally to reflect it in commonalities so in every API this pattern can be indicated in YAML.
        • Notification Model: Telefonica asks about behaviour of "notificationAuthToken" concept. Orange indicates it is a "Token" generated by client side and inserted as Authorization in notification from Payment server back to client. It is based in QoD model currently. Telefonica understands this and it comments this is not closed on its model so far (some solutions could be applied) and it is also not seen as the best approach to secure a notification. Ericsson also comments in that way. What is clear it is a common solution for any API is required, so probably it is a point for Commonalities WG. Orange shares view this is a topic for commonalities. Telefónica will check internally this. +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica contribution to deal with Issue 44 and Issue 47. Introduced from a high level poitn of view. Participants need to look into detail. Orange advises YAML seems to be some validation error. To be reviewed by Telefonica and update PR +Questions around APIs Proposals | • Q1-ERICSSON: Checkout - Management of Purchase LifeCycle: In Telefonica solution, an offline process runs to delete Purchases not attempted to be paid after some time. Other solutions could be marked them with an specific status. It depends also in Business Requirements.
        • Q2-ERICSSON: Checkout - merchant.fee: Why this param is mandatory when a given contract indicating this is signed in advance. Already queried and waiting response on it.
        • Q3-STC: Payment - Management of taxes: STC indicates it is needed in some way to indicate if an amount includes taxes or not. Orange comments "taxAmount" is an optional parameter in case merchant wants to indicate it. Ericsson porposes to have a boolean to indicate if "amount" has taxes. Orange requested Ericsson to open an issue to follow this.
        • Q4-STC: Both Proposals: Return transaction time of a payment in response (a timestamp). Need to Open an issue on it to detail and provide a way forward. It can make sense to have it.
        • Q5-STC: Checkout: Concept of merchant.id why is mandatory, because it may be identified by API client credentials (Orange for instance do in that way). Comment is in line of making it optional so only provided when merchant is different from API requester. Telefonica checks this in order to see if can be settled to optional adding an exception in case for any case it is required.
        • Q6-STC: Checkout: Offline questions raised to telefónica proposal. To be compiled in an issue to have track of them. + + +### Next Steps +- Next Meeting on 01st February diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0f0583b03a063057ff6414e6c77d814550c8bde1 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01/raw.md @@ -0,0 +1,51 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 01-feb-2023
        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Generate a Tag for v0.5
        +Review of Issues and Ongoing PRs
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment + + +### Items Discussion + +Item | Discussion +---- | ---- +Management Topics | Management of Users. Still not seeing in GitHub some collaborators. @Pedro contact Markus offline. DONE after the meeting +Generate Release Tag | Commented during meeting. Generate a Realease Tag to compile work done so far. No official version yet. Also versioning approach being discussed in Commonalities WG. DONE after meeting: https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.5.0 +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Comments provided by Orange about Glossary Definitions. Suggestions seen OK by Telefonica. New proposal about "Purchase" concept given by Telefonica. @ALL review thread. DEADLINE for this thread is EOW of Week 06. After that glossary proposal will be trigger into Commonalities WG +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | MERGED. Associated [Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) CLOSED +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange contribution to deal with Issue 44 and Issue 47. Given OK by Telefonica. Waiting any more comment during this week +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica contribution to deal with Issue 44 and Issue 47. Telefonica comments it is going to update based on output of some parameters that probably can be set as optional, so indicates to await until that is done to be reviewed. It will inform of that +Questions around APIs Proposals | Issues already created: Issues 54, 55, 56, managed as a set of tasklist +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica provided feedback to questions 2 and 4. Questions 5,6,7 currently being checked, probably there is room to set some params as optional. Questions 1 and 3 are pending from internal analysis. Regarding Question 1, Use Case is for instance a vending machine SW that needs to input user's msisdn to perform payment (based in a client credentials model, without involving user authentication) +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Orange comments it is ok about the issue and will provide a proposal in a next version. Commented during the meeting is is not urgent. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | After some discussion, it is discarded to indicate timestamps in requests to avoid inconsistencies and implementation complexity. At response level, it makes sense to have two "timestamps", date when the payment is created and date when the payment is effectively performed (optional). Summary provided by Orange in the issue with initial params proposal. +AoB | • **Notifications**: It is share common view that notifications management is a traversal topic. In this meeting besides notification securization is also mentioned how notification_url is provided. Currently, a dynamical approach is followed, also TMForum is referenced as other option (Registration of notification_url). About securization Telefonica indicates that, before triggering any discussion in CAMARA internal analysis has to be done from its side.
        • **APIs Family**: Ericsson comments about the topic of having only one approach (API favor) in this WG. Orange indicates that this should be the final picture in the WG, only having one option. Telefonica indicates it does not see opening this topic at least during this year, because currently is focused in providing new functionality to de BC Checkout proposal based on Business Requirements, although it understands it is the theorectical purpose of CAMARA of having a unique option for each track. Orange does not share the same view and thinks it is a topic to be analyzed in the short-term. + + +### Next Steps +- Next Meeting to be managed. Collision with Commonalities WG meeting, looking for a date after meeting diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b04578a77fac2ba5e79fa6e3c12a75a2b11c5255 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15/raw.md @@ -0,0 +1,51 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 15-feb-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String + + +### Items Discussion + +Item | Discussion +---- | ---- +Working Group Management | Rafał, Fahad and Nayeeem have already access into WG. Can be requested as reviewers. New member from STC presented in the meeting: Naeem Ur Rehman +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Proposed to be closed. Notifications model has relevance to be a traversal track in commonalities. Pending feedback from Orange that cannot attend meeting +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | If no further comments today/tomorrow, terms indicated with its meaning will be the ones proposed by Pull Request in Commonalities. Commented into WG for any final refinement or additional term. +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Proposed to be closed. Notifications model has relevance to be a traversal track in commonalities. Pending feedback from Orange that cannot attend meeting +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | MERGED. CLOSED +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | MERGED. CLOSED +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica still analyzing questions Q1 and Q3. Intention is to address them along with new API Proposal by TEF (covering 1-STEP and list of purchases). Probably MSISDN included, however under internal analysis. +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Indication in Payment approach whether amount has taxes. Targetted for a higher version. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Regarding payment relevant dates, proposal done by Orange.
        • Telefonica: indicates that makes sense the proposal and will include that info as optional. It is pending to discuss about inclusion in notifications body. Need also Orange's view on it.
        • Telefonica: taken advantage of this thread it is commented the need of align input/output parameters in snake_case format. That is something to guarantee by API proposals for v1.0. +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Keep this topic open until a common view of Error Model is aligned in CAMARA. API Proposals will have to be aligned in that way +AoB | • **Notifications**: Commented it is traversal topic. Telefonica internally working before open issue un commonalities (in a couple of weeks at least).
        • **APIs Family**: STC comments about the the topic of having only one approach (API favor) in this WG. Orange and Ericsson already commented last week they expect one API favor. Telefonica comments it is not seen in the short-term unless coming a guideline from "upper layers". Currently, both APIs have different concepts approach on how to address E2E behaviour. Also both APIs need to be aligned in terms of functionalities in order to check synergies in advance. + + +### Next Steps +- Next Meetings: Week of 27th February is MWC week
        + • 22th February (same datetime)
        + • 8th March (same datetime)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..370fb7f874588bdda82c2d06b2bbbc21b3e64470 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22/raw.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-feb-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml + + +### Items Discussion + +Item | Discussion +---- | ---- +Working Group Management | +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Set to CLOSED. +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Set to CLOSED. Contributed to [Commonalities Pull Request 120](https://github.com/camaraproject/WorkingGroups/pull/120) +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Set to CLOSED. +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica proposal to be presented yet, not possible to present this week due to internal matters. That is reason to keep Q1 and Q3 open. Indication of phone_number is foreseen as needed in some scenarios (WiFi, Fixed-Access, where mobile line can not explicitly identified by authentication process). When presenting proposal, rationale will be provided along with it. Ericsson also comments in this way, about the need of msisdn. Pending proposal by Telefonica, expectation is to have it during next week, so presented for the next meeting. +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Indication in Payment approach whether amount has taxes. Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Regarding payment relevant dates, proposal done by Orange. Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Keep this topic open until a common view of Error Model is aligned in CAMARA. API Proposals will have to be aligned in that way. Referenced in [Commonalities Issue 151](https://github.com/camaraproject/WorkingGroups/issues/151) +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Generated issue by Orange (separated from Issue 56, where initially mentioned). Commented by Telefonica that mention of align proposals is to be compliant with Commonalities in the way moving forward towards v1.0. Orange indicates they would like to open an Issue in Commonalities to discuss this topic, as there are other approaches in the ecosystem (OMA, TMF,...). Issue opened after meeting [Commonalities Issue 157](https://github.com/camaraproject/WorkingGroups/issues/157). +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56). Explained both dates (paymentCreationDate and paymentDate) are included as optional in GET /payments and /payments/{id}. Also paymentDate is included in notification, to indicate when payment is effective.
        • Ericsson is OK with the proposal as request coming from its side.
        • Telefonica is also OK with the proposal, and share view about including paymentDate in notification as it makes sense to have a coherente working proposal. + + + +### Next Steps +- Next Meetings:
        + • 8th March (same datetime)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..798da134c4c91af29787f23f63d4d9898d919eac --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08/raw.md @@ -0,0 +1,48 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 08-mar-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ziad H. (FOO.MOBI) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica provides answers for pending questions Q1 and Q3. Issue will continue open until WG review and give approval for [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60). Set to CLOSED. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) and Carrier Billing Checkout by [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64). Set to CLOSED. +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Commonalities Error Model is aligned in both proposals Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) and Carrier Billing Checkout by [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64). Set to CLOSED. +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Keep Opened. Being Evaludated in [Commonalities Issue 157](https://github.com/camaraproject/WorkingGroups/issues/157). Once taken a decision, actions will have to be performed within the proposals accordingly. +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56).
        • Minor update change clarified and performed by Orange (remove pattern for HTTP status) during the meeting.
        • Telefonica will review and give OK after the meeting. Ready to be merged +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | PR generated by Telefonica to provide functionality for 1-step payment and list of purchases. Besides this, it is taken advantage to also include:
        • `payment creation date` and `payment date` concepts in Details of a purchase and List of purchases endpoints.
        • In the same fashion, `payment date` concept is also included in notifications endpoint.
        • Additionally, `phone number` concept is included in payment body request (for both 1-step and 2-step procedures), as optional input, due to the fact in some authentication scenarios (e.g. Mobile Connect Based, Mobile IP based) phone number can be obtained and therefore that information can be carried within Authorization header. This does NOT mean an implementation can consider this parameter as required always but to explain the rationale of the proposal
        • Finally, HTTP `status` pattern is removed to be aligned.

        Mentioned to be reviewed by the WG team after the meeting to provide comments and further doubts.
        • Orange comments about two topics: The prevalence of the `phone number` request body param over Authorization information and in that way the scenario of having non-matching information between the value carried within this param and the information contained within Authorization header.
        • Telefonica indicates the information present in this param is the one to be considered when provided (so it prevails over Authorization header info) to identify the `phone number` to be charged and it is a very good point the one raised about non-matching information between this param and Authorization Header, so it will be reviewed internally. +AoB | Telefonica comments that given both proposals are moving forward to have an aligment at functionality level and pending points are mainly related to Commonalities topics (input/output params format, notificatons approach) it makes sense to move to a bi-weekly meetings model, work offline about proposals and Commonalities alignment and having specific weekly meeting if situation requires for it (relevant topic). Orange shares this view, given that proposals are reaching a common level of maturity and pending points to have a first set of functionality are related to Commonalities topics. WG considers suitable this WoW model and no objection raised. Meetings will be scheduled for the next two months. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting planned for 22th March (same datetime)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..99872e6f4f9439d3b5b0c76a3532fe3d4138ddbd --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29/raw.md @@ -0,0 +1,45 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 29-mar-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ludovic Robert (ORANGE) +- Naeem Ur Rehman (STC) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) +- Sönke Peters (VODAFONE) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Orange | Update Carrier_Billing_Payment_API.md + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Questions addressed and accordingly included in [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Commonalities Guidelines Updated and changes being considered within this WG PR60 and PR64. Set to CLOSED. +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56).
        MERGED. +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Updates regarding initial proposal: aligment with camelCase, includes pagination and exception when input phone number in payment does not match Auth context.
        To be reviewed by the WG up to 12/Apr.
        After its merging the same WoW will be done, updating related documentation. +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Update Documentation for Carrier Billing Payment v0.7.0.
        Reviewed by Telefonica (given OK). Additional comments to be received up to Monday 03/Apr. If no further comments, it can be merged Monday 03/Apr EoD. +AoB | • WG next actions: Move forward towards an initial v1.0 version for both proposals. Main pending topics are probably related to notifications topics (being managed in Commonalities).
        • Convivence of proposals: STC raised the topic, if there is a guidance from Steerco (rationale for them is to determine which proposal to implement). Telefonica indicates no news about it and from its point of view currently two proposals are in force. Oranges shares the view on deciding about one proposal and not only regarding this WG but also another WGs (Number Verification,...). Telefonica will check internally + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Pedro to align with Jose Antonio Ordoñez Lucena to avoid overlapping with IdentityAndConsentManagement WG meetings. DONE offline after meeting
        + • Next meeting proposed to be on 13th/April - 12:00 CEST
        + • Rest of scheduled meeting series do not overlap with IdentityAndConsentManagement WG
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3ff11803f997d00a30a5504bb1979ce2e83b3398 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13/raw.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 13-abr-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Orange | Update Carrier_Billing_Payment_API.md + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Questions addressed and accordingly included in [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64).
        Set to CLOSED as covered in Pull Request 64. +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Update carrier_billing_checkout_1-step_model_and_purchases_list (v0.7.0 aligned in features with Payment proposal). MERGED
        After its merging the same WoW will be done, updating related documentation. +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Update Documentation for Carrier Billing Payment v0.7.0. MERGED + + +### AoB + +WG next actions:
        + +• Notifications Guideline Track (initial baseline) is being completed within [Commonalities PR#173](https://github.com/camaraproject/WorkingGroups/pull/173). Once completed, main pending point is to address impact/discussion in current notifications approach. Probably better way is an issue to open discussion over it, before proposing any change if any. That is main point to move proposals towards a v1.0 (apart from documentation topics).
        + +• Documentation track: Pending to incorporate into OpenAPI proposals full autocontained documentation model as per [Commonalities Issue#164](https://github.com/camaraproject/WorkingGroups/issues/164). Orange highlights made a question about images, and it seems it can be possible (in Carrier Billing there are sequence diagrams). Both Orange and Telefonica will make tests to check all information can be accommodated within OpenAPI yaml.
        + +• Convivence of proposals: Telefonica has commented internally, in order for Business to be aware of situation and for them to be able to do product checkings and also has contacted to have business contacts from some Telco Operators.
        + +• STC indicates they have some concerns about the proposals and will make some contribution regarding it. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting - 26th April - 16:00 CEST diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..28acb160555200192e4e8fa53c5f0358d14235d8 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 26-abr-2023
        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan (ERICSSON) +- Ludovic Robert (ORANGE) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) +- Claudio Di Padova (VODAFONE) +- Mariusz Dawidowicz (VODAFONE) + + +## Goals +Review of Issues/PRs and next steps
        + +Item | Who | Description +---- | ---- | ---- +Welcome to newcomers | WG | New attendants within WG:
        • Jorge García Hospital (TELEFONICA): Product Owner of Telefonica in GSMA OpenGateway initiative.
        • Claudio Di Padova (VODAFONE): VF Germany Product owner for Payment products (among other features).
        • Mariusz Dawidowicz (VODAFONE): Product Manager in VF regarding Charging Services +[Issue 69](https://github.com/camaraproject/CarrierBillingCheckOut/issues/69) | WG | Manage Documentation +[Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70) | Telefonica | Fake PR to test model for inclusion of images + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 69](https://github.com/camaraproject/CarrierBillingCheckOut/issues/69) | Test successfully performed within [Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70), we can move forward. In order to move forward Pedro will comment within [Commonalities Issue 164](https://github.com/camaraproject/WorkingGroups/issues/164) and will wait for Commonalities output before to update the documentation +[Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70) | Fake PR to test model for inclusion of images within "description" field of API dcoumentation. CLOSED after meeting +AoB | **Subscription (within Notifications Commonalities Track):**
        • Discussion on Subscription path still open - Ludovic will modify the PR and send back to review to Artych, Pedro & Eric.

        **Other topics:**
        • Pedro explained existing flavors managed in the project.
        • Pedro and Telefonica is working on an aggregated proposal and will reach Orange for finding a consensus.
        • Question on business/product side: this is driven in a GSMA Open Gateway Business stream (not a CAMARA project). + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting 10-may-2023
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6c1d9ba2a3cfc3c7192e378683715f7db419f18d --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24/raw.md @@ -0,0 +1,34 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 24-may-2023
        +**Status:** FINAL + +## Attendees +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG | Decision in CAMARA API for Carrier Billing +[Several Issues] | Huawei | Several Issues Opened by Huawei (Miranda Tsing) more details below + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Issue opened based on topics/discussion already kept within WG.
        • Orange (Ludovic) could not attend meeting but advised in advance about the opening of the issue. Agreed to upload [PR#78](https://github.com/camaraproject/CarrierBillingCheckOut/pull/78) as supporting documentation.
        • STC looks good to open the issue and be able to manage this topic as it is needed an aligned solution.
        • Commented during meeting, with the aim of reaching a conlusion and have a way forward within this WG.
        • Being internally checked also with Markus under which conditions a votation can be performed within WG or needs to be addressed via TSC.
        • After meeting (26/May), Orange indicates their preference of managing this topic at TSC level. +[Several Issues] | Several Issues opened by Huawei. Company is interested in contributing in this WG. Issues to be addressed offline during next two weeks (Issues 73, 74, 76, 77). Miranda joined meeting once finished. Pedro talk to her offline in order to comment about next meeting so she can join, introduce herself into the WG and participate in meetings. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting 7th June (To Be Scheduled). 16:00 - 17:00 CEST
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..00dac4df3ed221d9bdffecc7c71a6845e4fb8a2c --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-jun-2023
        +**Status:** FINAL + +## Attendees +- Toyeeb Rehman (GSMA) +- Ajit Raghavan (ERICSSON) +- Elisabeth Mueller (ERICSSON) +- Shuting Qing (HUAWEI) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Ad-hoc meeting to present joint Orange-Telefonica proposal
        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG | Decision in CAMARA API for Carrier Billing +[Issue 87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Orange-Telefonica | Joint Carrier Billing Proposal +[Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica | ORA_TEF_CarrierBilling_joint_proposal-Issue87 + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Issue CLOSED. Agreement reached between Orange and Telefonica. New Proposal presented +[Issue 87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Rationale for the agreement and joint proposal presented by Orange and Telefonica. Compiles the basis and key pòints for the new proposal. Kept open until [Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) is merged. +[Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica joint proposal. Proposal explained. Main output points:
        • Good reception by WG members which consider a good starting point to move forward within WG.
        • Some adjustments to be performed after proposal presentation (To be documented in PR description for transparency), regarding error scenarios. **AP@Pedro Díez** to manage opening of topics/issues in Commonalities (Link HTTP 400 to OUT_OF_RANGE, Fixed INVALID_ARGUMENT typo).
        • Ericsson asks for rationale of making phoneNumber opctional. There can be scenarios where phoneNumber can be identified via Access Token (i.e Authorization header info). Anyway it is an open topic in GSMA OGW how to align access to APIs.
        • Ericsson asks for enabling the filtering of payments associated to a given merchant. Orange indicates in initial proposal "fields" value was supported. Telefonica comments that in this case what it is needed is to only return payments related to a given condition not related to only return some fields of the response. Seen as valuable point to address. **AP@Ludovic** to open issue in Commonalities.
        • PR open for comments in the next week. Aim is to merge this initial proposal on 12th July week. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting TBD. **AP@Pedro Díez** to propose dates for summer period
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eb4da95fb67912e68d8c57f40d7a928aaa9f4ae4 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19/raw.md @@ -0,0 +1,53 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 19-jul-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ajit Raghavan (ERICSSON) +- Masaharu Hattory (KDDI) +- Ludovic Robert (ORANGE) +- Philip Lengyel (TELEFONICA GERMANY) +- Agustín Martín (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Orange-Telefonica | Joint Carrier Billing Proposal +[PR#88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica | ORA_TEF_CarrierBilling_joint_proposal-Issue87 +[PR#81](https://github.com/camaraproject/CarrierBillingCheckOut/pull/81) | Huawei | revise meeting info +[Issue#73](https://github.com/camaraproject/CarrierBillingCheckOut/issues/73) | Huawei | Update Github PR Template +[PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72) | Huawei | Github PR Template +[Issue#76](https://github.com/camaraproject/CarrierBillingCheckOut/issues/76) | Huawei | Business Scenario for Carrier Billing Check Out +[PR#75](https://github.com/camaraproject/CarrierBillingCheckOut/pull/75) | Huawei | Add a business scenario slide +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Telefonica | Summer Meetings Planning +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Ericsson | Improvement suggestions for merged API + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Rationale for the agreement and joint proposal presented by Orange and Telefonica. Issue CLOSED. [Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) is merged. +[PR#88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica joint proposal. MERGED to have initial proposal to move forward +[PR#81](https://github.com/camaraproject/CarrierBillingCheckOut/pull/81) | revise meeting info. Updated meeting Info. MERGED +[Issue#76](https://github.com/camaraproject/CarrierBillingCheckOut/issues/76), [PR#75](https://github.com/camaraproject/CarrierBillingCheckOut/pull/75) | Business information provided by Huawei. Commented it fits better within GSMA OGW initiative. CLOSED +Generic Note | Commented in meeting that summary of Issues/PRs being carried in the last month will be reflected to have track of progress, even not mentioned / discussed in meeting. See topics above. Also, it is indicated a new issue will be opened (Telefonica) to compile documentation that has to be deleted/updated according to existance of a common proposal. +[Issue#73](https://github.com/camaraproject/CarrierBillingCheckOut/issues/73) | Update Github PR Template. Issue to inform about adapting GitHub templates defined in Commonalities to Carrier Billing Working Group. Being carried in [PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72). CLOSED after meeting +[PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72) | Github PR Template. Some adjustments commented by Rafal (bug template and labels) and performed respectively by Shuting and Pedro. After meeting, "bug template" is removed and PR is MERGED.## +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Commented planned dates for the next meetings. Bi-weekly period to be recovered in Autumn. Ericsson and Orange indicates dates are fine for them. No objections. Next meetings will be scheduled accordingly. Huawei provided comments within this issue, however does not attend the meeting. If any comment, it will be driven within the issue. +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Issue opened By Ericsson with the aim of defining valuable filter criteria for the GET /payments endpoint. Some initial comments by Ericsson, Orange and Telefonica compiled in issue. Discussion about filtering:
        • First, we need to provide mechanism to 'waterproofing' between API client. Technical credential could be used for that but it must be documented. Ludovic (Orange) will raise the point to commonalities as this 'data sealing' must be done for any API providing a capability to retrieve a list. Pedro (Telefonica) comments that this logic makes sense within carrier billing, due to it may compromise privacy and legal implications that a given API client can kave access to payments triggered via a different one and not sure about the traversal applicability of this in other tracks, anyway open an issue in commonalities is fine to have traversal view about this.
        • Second, for specific carrier billing filtering criteria, Pedro will create a PR to get consensus within working group for a set of criteria. Ajit (Ericsson) provided some suggestion within the meeting. +AoB | Ajit (Ericsson) raised a point about tax: if `isTaxIncluded` is false how the tax is computed? In this case the BE system will require the service (and product) id to calculate tax accordingly. This is an implementation issue to be sure service id (and product id) are related to tax code.

        Management of recurring payments and refunds - Need to be discussed in the product stream (not prioritized right now). Pedro (Telefonica) will create 2 issues to collect feedback for Refund and for Recurring Payment respectively. + + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meetings: 23th-AGO, 06th-SEP
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bd7bf00de4286cf50f12aded5ccc82799eca2147 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23/raw.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 23-aug-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Telefonica | Summer Meetings Planning +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Ericsson | Improvement suggestions for merged API +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Telefonica | Documentation Update in Carrier Billing WG +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Dates already managed. Next meeting September, 6th will be moved one hour later than planned (17:00 CEST) to avoid collision with Identity/consent WG meeting. In that meeting, it will be talked about resume bi-weekly meetings. CLOSED +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Related [PR#96](https://github.com/camaraproject/CarrierBillingCheckOut/pull/96) generated few weeks ago.
        Main topic addressed is adding filtering attributes (using commonalities design guideline 'grammar') in `GET /payments` operation, and also align description for date-time fields format. `paymentCreationDate` is set to mandatory in response model. During the meeting it is commented that some adjustment is needed with regards to the date filtering to be more explicit. Pedro will do after meeting. If no further comments PR will me merged in one week from now.

        We propose to keep the version in 0.2-wip as changes are coming on notification in particular for notification format (specific or cloud event) and for the introduction of using callback (like in qod). +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Documentation Update in Carrier Billing WG. Issue opened to manage WG repo updates with current "picture" status. Already covered 3 of 4 tasks. Related actions/PRs:
        • WG renaming discarded after checking with Markus (huge effort). DONE/CLOSED.
        • [PR#94](https://github.com/camaraproject/CarrierBillingCheckOut/pull/94). Move old proposals to `/documentation/supportingDocuments` folder. DONE/CLOSED.
        • [PR#95](https://github.com/camaraproject/CarrierBillingCheckOut/pull/95). Update `README.md` at 'root' directory. DONE/CLOSED.
        • Update documentation in `/documentation/API_documentation/` folder. Pedro and Ludovic will check offline to identity documentation to be updated and generate subsequent PRs required. OPEN. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Two topics raised:
        • Enhancement of the look & feel. Pedro (TEF) makes a proposal for a better look & fell for the errors. Ludovic (ORA) indicates is probably good to see how is it described in other API and in particular in QoD and perhaps propose a same look & feel across all APIs. Pedro will also check APIs in other WGs. Rafał provides also reference to Commonalities Issue [#31](https://github.com/camaraproject/Commonalities/issues/31) within this context.

        • Notifications design. Related to Commonalities Issues [#8](https://github.com/camaraproject/Commonalities/issues/8) and [#44](https://github.com/camaraproject/Commonalities/issues/44). Based on agreement reached, probably would be needed to re-design notification endpoint. That is also reason to keep current version as v0.2.0-wip. Ludovic (Orange) comments is reasonable this way forward. +AoB | • Mohammed (STC) asks about Token lifetime conventions. Both Ludovic (ORA) and Pedro (TEF) comments that this topic is a matter of implementation and up to security considerations in each Operator.
        • Mohammed (STC) also asks about recurring payments functionality. Pedro (TEF) indicates currently the WoW is for new features to be agreed in GSMA Open Gateway before going to CAMARA. In case of TEF and ORA there is also interest and TEF is considering/pushing this in GSMA. Pedro will provide Mohammed contact with TEF/ORA product members. + +### Next Steps +- Next Meetings:
        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
        + • Next meeting: 06th-SEP, 17:00 - 18:00 (CEST)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0efbffd16088b658edaa901d905729244bfe8af8 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06/raw.md @@ -0,0 +1,37 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-sep-2023
        +**Status:** FINAL + +## Attendees + +- Masaharu Hattori (KDDI) on behalf of Toshi +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Update Working Group Status +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Telefonica | Documentation Update in Carrier Billing WG +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#101](https://github.com/camaraproject/CarrierBillingCheckOut/issues/101) | Orange | Fix `x-correlator` type (should be `X-Correlator`) + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | So far, **initial v0.2.0-wip is merged** including mainly filtering rules to common proposal. Next steps are dependant on output from commonalities (Notifications, securitySchemas, datetime format,...). It is expected to begin to work in a consistent v0.2.0 at the end of september so as it probably can be tagged as the first release of Carrier Billing (will talk at that time). +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Documentation Update in Carrier Billing WG. Work offline between Orange (Ludovic) and Telefonica (Pedro) to manage pending actions and distribute work. 2 PR have been triggered:
        • [PR#99](https://github.com/camaraproject/CarrierBillingCheckOut/pull/99) to remove documentation no longer required - some documentation will be removed once we complete the yaml documentation of the API spec.
        • [PR#100](https://github.com/camaraproject/CarrierBillingCheckOut/pull/100) to remove checkout word + update Model.
        Both PRs were cross-reviewed by Ludovic and Pedro respectively and gave OK. They have been MERGED after the meeting. Issue is CLOSED. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Two topics raised:
        • **Enhancement of the look & feel**. Pedro indicates not able to address look&feel situation in other APIs. So Look & feel across API will be done later and resume this topic of the issue.

        • **Notifications design**. Waiting to commonalities outcomes. Related to Commonalities Issues [#8](https://github.com/camaraproject/Commonalities/issues/8) and [#44](https://github.com/camaraproject/Commonalities/issues/44). Pending on the output of those issues, related PRs are [Commonalities-PR#43](https://github.com/camaraproject/Commonalities/pull/43) and [Commonalities-PR#56](https://github.com/camaraproject/Commonalities/pull/56) respectively. +[Issue#101](https://github.com/camaraproject/CarrierBillingCheckOut/issues/101) | Understood the rationale of the issue. Pedro (Telefonica) comments HTTP headers are case insensitive so both Uppercase and lowercase are valid. Ludovic (Orange) closed the issue after the meeting. Issue is CLOSED +AoB | • STC (Mohamed E. Ali) wishes to get business discussion on new features (refund, recurrent payments) - Pedro (pedro.diezgarcia@telefonica.com) will make Mohamed in contact with TEF (Agustin) & Orange business (Patrick Berthie).
        • Next meeting Sep, 28th (at 4.00 CEST) and then get back on nominal schedule from Oct, 11th + +### Next Steps +- Next Meetings:
        + • Next meeting: 28th-SEP, 16:00 - 17:00 (CEST)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fa7abcd01940f560d47b3d74d92f276eabf90213 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28/raw.md @@ -0,0 +1,33 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-sep-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Update Working Group Status +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Next steps are to work in a consistent v0.2.0, addressing several issues:
        • Commonalities related: securitySchemas, notifications guidelines.
        • Enhancing API documentation in API spec.
        • Fixing some topics (e.g. adding 404 Exception to endpoints that have paymentId defined in path) and gaps.
        Several issues will be opened and reuse a common PR to work on. Some comments from Ludovic (Orange) about securitySchemes for query endpoints (GET) to be used in 2-legged mode, to be discussed further. With all of this, an initial release would be tagged. Rafał (DT) also comments in this way in order to have an initial release. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Regarding the topic of **Enhancement of the look & feel** Pedro (TEF) will take a look to other WGs next week. Regarding **Notifications design** it will be addressed with commonalities output. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 11th-OCT, 16:00 - 17:00 (CEST)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..569ba976cafd423b50a02d658eb6841353970dd9 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11/raw.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 11-oct-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | External | Refund functionality for Payment requests +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Deutsche Telekom | Type representing money values +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Telefonica | Enhancement of Documentation within API OAS yaml +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Telefonica | # Add 404 Exception to other API endpoints that have {paymentId} in API path +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Telefonica | API Spec aligment with Commonalities securitySchemes, security and scopes +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Orange | Align Carrier Billing Event with CloudEvents structure + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Limited scope to topic of **Enhancement of the look & feel** (Notifications aligment covered in [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112). Action Point to Pedro to provide info to the WG. Deadline is 16th October +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | Issue opened externally. Good to be tracked. Fair request from a technical perspective.
        • TEF (Pedro) comments in advance TEF Product side will probably ask for this functionality during this year.
        • ORA (Ludovic) will also check for Product view internally.
        Commented during the meeting the product side could be trickier (depending on country regulations for example). Need to be addressed after tackling current issues in progress. Comments from the team are welcome. Need to synch with GSMA OGW product stream which manage API requirement drop.
        • STC (Mohamed) raised a question about managing technical issue where we have several payments for same interaction. Scenario can be managed with the use of the `clientCorrelator` field so as we should not have this problem.
        • STC (Mohamed) also explained the requirement for reversal vs refund. There are distinctions between reversal (time-limited, in case of STC is End Of Business Day, this is to reverse a payment, the merchant will not get charged for this) and refund (this is a new transaction independent from a payment, merchant is charged for that). This is a good point for Refund thread. Action Point for Mohamed to comment in the issue. +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | DT (Rafał) introduces the topic. It aims for modeling amounts in a way it may be used worldwide, allowing to tackle the disparity of decimal (0,2,3) in different countries around the world. Proposal here is to use long integer for amount and depending on the currency we deduct the decimal. WG agrees to gather more feedback on this issue and continue discussion. +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Issue to deal with Commonalities guideline of having full API documentation within API Spec. TEF (Pedro) will use our initial Markdown documentation & incorporate it (and refresh) in the yaml, generating a new PR. Further updates would be required based on output of other issues discussion (e.g. [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110)). Agreed by the team. +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Issue opened to reflect the fact that other endpoints (`preparePayment`, `confirmPayment`) has the same scenario of a non-existing Payment Identifier as `retrievePayment`, so 404 NOT_FOUND exception is needed. Agreed by the team, to be handled in same PR than [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106). +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Dealing with two Commonalities topics alignment:
        • **securitySchema**: need to wait Commonalities (or TSC) outcomes - Commonalities PR: [Commonalities#57](https://github.com/camaraproject/Commonalities/pull/57).
        • **scopes**: we can go with the way proposed in the issue and proceed within the same PR. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Issue driven by implementation feedback. Case risen due to the fact no filter criteria is mandatory to be provided, to have an alignment about given response. Use of page/perPage is defined Commonalities. The proposal here is to provide default value, so we can also improve performance in the response time.
        • ORA (Ludovic) indicates we need probably another error code when the request is too vague/wide (too many records match the filtering criteria), for instance, payments whose "transactionOperationStatus" is equal to "succeeded". Given also the fact the initial baseline was to return all registries when no filter criteria was indicated. Additional thinking is required regarding this issue. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Trigger is the identification of "denied" scenarios in 2-STEP Payment (i.e. user is blocked when trying to confirm payment). Based on that, also other points are covered for alignment of lifecycle understanding. Further discussion / thinking is required on this. Some points compiled so far:
        • Exception 403 Payment Denied for two-step confirmPayment
        • Discussion on sync one-step payment: probably the only state is succeeded when the payment resource is created while for async we can have Denied (from Processing state). This is not reflected on the current state engine.
        • A new event is required for Payment denied. Team agreed.
        • Discussion about when the balance is checked for the two-step payment: When the payment is `reserved` the money is blocked. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Not covered during the meeting. To be handled in next meeting. Kindly ask offine review. +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | ORA (Ludovic) remarks the need of Notifications alignment with commonalities. It is needed to be covered. Agreed by the team. To be considered within PR. Pedro and Ludovic will talk offline to manage PR(s) in the best way. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 25th-OCT, 16:00 - 17:00 (CEST)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4b4d20ee46dd8bc820a974fa9f7edbceb842ddd2 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25/raw.md @@ -0,0 +1,58 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-oct-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | External | Refund functionality for Payment requests +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Deutsche Telekom | Type representing money values +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Telefonica | Enhancement of Documentation within API OAS yaml +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Telefonica | # Add 404 Exception to other API endpoints that have {paymentId} in API path +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Telefonica | API Spec aligment with Commonalities securitySchemes, security and scopes +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Orange | Align Carrier Billing Event with CloudEvents structure +[Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114) | STC | Identify if the payment is one time payment or recurring payment +[Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) | STC | Reversal API +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | TEF | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | TEF | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Limited scope to topic of **Enhancement of the look & feel**. Action Point to Pedro to provide info to the WG. Feedback provided and documented in the issue, identifying in main relevant CAMARA API the model with specific object schema is used for specific Exceptions. Therefore, adopting this model in Carrier Billing as well. Agreed by the WG and it will be **integrated in next PR**. +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | This feature will be addressed later, after having consistent 1-STEP and 2-STEP Payment models. +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Telefónica provides internal analysis, indicating current billing systems works naturally with "decimals", so this model would have huge impact. Orange thinks the same, will check internally for confirmation.
        Nevertheless the issue points the topic of addressing 3 decimals in some currencies/countries, so we need to redefine `amount` model to have 3 digits to cover some UC (i.e. worldwide interoperability). This can be done by indicating `multipleOf: 0.001` in `amount` format as this concept in OAS3 indicates the step between two consequent values, so up to 3 decimal digits can be addressed (NOTE that 5,450 is equal to 5,45 OR 6,000 is equal to 6, as float covers integers per definition). In addition to that, an implementation could specifically throw error if they manage 0, 1 or 2 decimal. Agreed on this way forward. It will be **integrated in the next PR**. +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Dealing with two Commonalities topics alignment:
        • **securitySchema**: mention to openId connect could be done in the yaml with the notice that this is not yet completely validated. Discussion ongoing in Commonalities and Identity&Consent Management.
        • **scopes**: scope will be **integrated in the next PR**. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Issue commented during last meeting. Pedro comments besides indicating page, perPage default values in API spec, it makes sense to have an exception to manage uncoherent situations from API Server side (invalid params combination). Ludovic nuances the comment was not about wrong combination but to send an exception when too many record matches, and it will provide feedback within the issue. Discussion continues in the Issue before taking next steps. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | So far, potential impacts identified are:
        • Exception 403 Payment Denied for two-step confirmPayment
        • New event for Payment denied.
        However, in order to not missed anything, it is better to detail the status transitions in every scenario (1-STEP and 2-STEP), so we get two objectives:
        • Having an aligned understanding of the status transitions and document it within API. Identify design actions in the API (new events, exceptions,...).
        • Identify whether state machine needs also to be updated.
        Pedro will draft some documentation within the Issue for alignment and discussion. Discussion continues in the Issue before taking next steps. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica comments the issue in order to indicate the feature of retrieve payment(s) refer to the context of a given phone number. Orange comments there are also Use Cases where API client (App) can obtain information not on behalf of a given user phone number. In API there is no phone number as parameter. This topic requires more discussion and aligment. Comments are welcome for the next meeting. +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114) | Initial discussion during the meeting. STC comments the issue indicating it has both business and security implications:
        • For recurring payment the OTP will not be required.
        • Security perspective, having impact in Token lifetime.
        Orange indicates this process is managed first with the creation of a product order that represents the subscription and after that, periodical post payments are performed.
        Telefonica indicates probably the Business view on this procedure may be different in Telco Operators so an aligment from Product Perspective is probably required in GSMA OGW product track to have guidance on this matter. +[Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) | Issue introduced during last meeting. Telefonica has commented internally to Business due to the relationship with Refund procedure, as they are elaborating the refunds requirements. In the same fashion as former issue, it is probably required an alignment in GSMA OGW product track to have guidance on this matter. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Not covered in the meeting. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | Not covered in the meeting. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 8th-November 16:00 - 17:00 (CEST)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3062b7fab0f1699d7bf70402e45990aea85eb3fa --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08/raw.md @@ -0,0 +1,44 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 08-nov-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[PR#120](https://github.com/camaraproject/CarrierBillingCheckOut/pull/120) | Deutsche Telekom | Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Telefonica | Enhancements for Carrier Billing v0.2 - Part I +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | TEF | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | TEF | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#120](https://github.com/camaraproject/CarrierBillingCheckOut/pull/120) | PR triggered by Deutsche Telekom (Rafał) in order to align WG repository with the guidelines of CAMARA regarding [Testing Folder](https://github.com/camaraproject/Template_Lead_Repository/pull/1). Reviewed and approved by Orange and Telefonica. `MERGED` during the meeting. +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Pull Request triggered to cover Issues: [Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97), [Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105), [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106), [Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107), [Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108), [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112). Explained during the meeting the impacts in API yaml spec. Main points covered:
        • Enhance the documentation (from previous documentation & other APIs).
        • Alignment for security scheme & scope. We have distinct scope for create the payment (create), for confirm/cancel in 2 steps (write) and a third (read) for getting the data.
        • Notification alignment with CloudEvents model (QoD/Device Status used as template/references).
        • Added 404 for confirm/cancel payment.
        • Amount precision with 3 decimals.
        Some comments already provided by Ludovic (Orange) and Rafał (Deutsche Telekom) to be managed. They will check/review in deep during the next days. Regarding the point about "x-correlator" it will be managed within Commonalities. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica proposal indicated within the issue is agreed by Orange. Therefore this issue will be **managed in the new next PR**. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Explained the output identified so far in the issue:
        • New event type "denied".
        • New event type "pending_validation" (in the joint anaylisis per [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116)).
        • New Exception 403 CARRIER_BILLING.PAYMENT_DENIED in some operations (this also addresses [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117)).
        Open point: Having a specific attribute for "denied" reason. Work offline to compile common cases.
        Issue will be reviewed by Orange and Deutsche Telekom. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica proposal (approach 1) looks good for Orange. Deutsche Telekom will review offline. It mainly implies documentation but Telefonica (Pedro) will check if additional error should be managed. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Explained the rationale/objective of the issue during the meeting. There may be business scenarios in 2-STEP Payment whether OTP validation procedure is required (because UI associated to OTP validation is built by merchant). Therefore, it is proposed an enhancement in `preparePayment` response regarding validationInfo model and also a new optional method validatePayment. Associated state transitions are also mentioned within the Issue. NOTES:
        • State change lifecycle diagram must be reviewed.
        • (1STEP/2STEP) should be added in all transitions (missing on the first 2).
        Issue will be reviewed offline by Orange and Deutsche Telekom. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | It will be managed with the [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) so as no new exception would be required. +AoB | WG objective:
        • Carrier Billing v0.2.0 Release Candidate will cover all these points handled during today's meeting.
        • Refund & other function will be cover in following release. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 21st-November 11:00 - 12:00 (CET)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9e8db075bb824095781c679d3fbd65eab10b8ee8 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21/raw.md @@ -0,0 +1,44 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-nov-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) +- Benedikt Blome (Vodafone) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Telefonica | Enhancements for Carrier Billing v0.2 - Part I +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Telefonica | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | Telefonica | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Pull Request triggered to cover Issues: [Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97), [Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105), [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106), [Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107), [Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108), [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112).
        Pull request is `MERGED` so as related issues are `CLOSED`. This is the first of the two PRs in order to reach a stable v0.2.0 version. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | WG Agreement for this issue to be **managed in the new next PR**. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Impact already identified is aligned:
        • New event type "denied" (probably suitable wording is payment-denied).
        • New event type "pending_validation" (in the joint anaylisis per [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116)).
        • New Exception 403 CARRIER_BILLING.PAYMENT_DENIED in some operations (this also addresses [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117)).
        During meeting open point about "denied" event is aligned and optional parameter to indicate denialReason (string) is agreed to be considered. Then, this issue will be **managed in the next PR**.
        Ludovic (Orange) also comments that currently we have only implicit subscription so adding this denialEvent is fine, but to keep in mind that if we add explicit subscription pattern in future then we can assess event type granularity:
        • Keep event type per state or
        • Have one generic event type for payment state change. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica proposal approach 1 is seen as better approach. Regarding if additional error should be managed, Pedro (Telefónica) explains the case for FrontEnd Flow (auth_code) -not for Backend Flow (CIBA)- in case we are unable to get the phoneNumber from the access token or if the phoneNumber retrieved from the token is distinct from the one is the payload, so as new 403 Exception is considered (Details in Issue). Ludovic indicates it is fine to consider this case. Then, this issue will be **managed in the next PR**. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | This issue was covered in the last meeting. Very small request from Ludovic (Orange) to add (1S/2S) in first 2 transitions diagram clarified during the meeting. Pedro will update source code and image within the issue and will trigger a specific PR for the diagram so as link can be used directly. This issue will be **managed in the next PR**. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | It will be managed with the [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) so as no new exception would be required. +AoB | **WG objective:**
        • Carrier Billing v0.2.0 Release Candidate covering all these points handled during today's meeting.
        • Refund & other function will be cover in following release.

        **Test definition:** Topic commented by Rafał (Deutsche Telekom) and Ludovic (Orange) It will be required to address the test definition in this WG but first need to have a global agreement of the format for the test definition. [Commonalities/Issue#94](https://github.com/camaraproject/Commonalities/issues/94).

        **Test Filtering GET**: Topic commented by Rafał (Deutsche Telekom), [Commonalities/Issue#10](https://github.com/camaraproject/Commonalities/issues/10), [Commonalities/PR#82]([https://github.com/camaraproject/Commonalities/pull/82). Discussion on the filtering criteria, Rafał has prepared a PR in commonalities based on the issue opened. Pedro indicates from Telefónica side it was alignment with Rubén, so as (`gte,gt,lte,lt,eq`) applies for both numeric and dates but no makes sense for enumerated fields (only eq). Rubén also proposed `neq` as the opposite of `eq`. There is some discussion on alignment with TMF pattern (TMF Forum works with URL encoded value of `logical condition` but in CAMARA we are adding suffix to the filtering criteria parameter when applicable. Ludovic raised the point of discrepancy risks between CAMARA & Operate from Channel partner perspective and will also comment in Commonalities issue.

        **Next Steps**: Meeting in 4th December week will be moved to 12th-December (Pedro is on holidays that week) and if needed meeting in 18th December week will be hosted. In the meantime, new PR will be triggered (Pedro) to cover pending points at least during 27th November week in order to have time for its review. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 12th-December 11:00 - 12:00 (CET)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..11fd5f2b1b53859da44c2e2f00e46ebc1890cd71 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12/raw.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 12-dec-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Laurent Grandin (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Telefonica | Enhancements for Carrier Billing v0.2 - Part II +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Pull Request triggered to cover Issues: [Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109), [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110), [Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111), [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116), [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117).
        Reviewed by Ludovic (Orange). Comment provided regarding the fact in 1-STEP Payment, SYNC behaviour, `denied` status is not reached, so lifecycle diagram needs to be updated. Pedro (Telefonica) agrees on that, because in such a case an exception would be triggered instead. **AP:** Generate a new PR to update lifecycle diagram so as it can be integarted in current [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125). Intention is to have it in this week, therefore to be able to merge it during next week. +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Issue opened by Ludovic (Orange) to deal with Commonalities linting rules track. Rafał (Deutsche Telekom) already explained context in today's Blockchain Public Address WG meeting, so as Pedro (Telefonica) is also aware of that. Assigned to Pedro. Next Commonalities meeting is in 4 weeks, so enough time to check. +AoB | Laurent Grandin (Vodafone) joins WG meeting, he has worked in Carrier Billing/Payment solutions in Vodafone during the last ten years.

        **WG objective:**
        • Carrier Billing v0.2.0 Release Candidate to be generated after [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) merge.

        **Next Features**: Have some slot in the next meeting (20th December) to begin to talk and share views on new features: Refund - [Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104), Recurrent Payments - [Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114), Reversal procedure - [Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) + + +### Next Steps +- Next Meetings:
        + • Next meeting: 20th-December 15:00 - 16:00 (CET)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9f88209f09f3f025321092648ded4023cf860849 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20/raw.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 20-dec-2023
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Agustín Martín (Telefonica) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Telefonica | Enhancements for Carrier Billing v0.2 - Part II +[PR#128](https://github.com/camaraproject/CarrierBillingCheckOut/pull/128) |Telefonica | Diagram Payment Lifecycle Adjustment +New Carrier Billing Features | WG | Kick-Off about new Carrier Billing Features + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Pull Request need final review from the team. Ludovic (ORA) approved it as already reviewed. Please make comments if any. Intended to merge this week. Once this done, Pedro (TEF) will create another issue to create the rc version (The version will be suffixed with -rc). Then Pedro will do a PR with the swagger updated with this version. But merging PR #125 is a prerequisite. Accordingly, Pedro will do a PR with the swagger updated with this version. Final comments can be indicated over this new PR. +[PR#128](https://github.com/camaraproject/CarrierBillingCheckOut/pull/128) | Pull Request generated in order to address Ludovic's comment in [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) about not reaching `denied` status in 1-STEP PAYMENT, SYNC process, already `MERGED`. +New Carrier Billing Features | Discussion for new functionalities. Pedro (TEF) listed them:
        • Refund
        • Recurring payment
        • Reversal (This is for temporary transaction so this is a rollback without any charge to the customer)

        Priorities from the community:
        • For DT, needs to check with product team
        • For Orange, needs to check with product team
        • For STC, needs to check with product team
        • For Telefonica, it is refund

        **Zoom on Refund function** by Agustin (TEF) [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104))
        • Refund could be total or partial.
        • Additional state could be added.

        Initial Comments:
        • Ludovic indicated was not aligned from model to have a ‘same’ resource for both payment/refund. His preference is to have separated resources.
        • Mohamed (STC) has some UC where the payment id is not mandatory in the refund (Merchant is in charge to control de balance/accountability of the transactions). Ajit (ERICSSON) agreed on this. Question raised is: then, how the refund is correlated to the payment? Not necessary, Mohamed explained that this is the difference with reversal whom mandate payment.
        • Agustin explained that in Telefonica the refund must be correlated to one payment (not more than one), but the refund could be less than the initial payment amount, so as it is possible to have several refunds for same payment as long as the sum of the refund did not exceed initial payment amount.

        **Zoom on recurring payment** by Mohamed (STC) [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114))
        • It is explained as a feature to differentiate one-time payment from recurrent ones so as OTP is no required from the subsequent payments. In terms of Backend logic is enable internally a periodic payment without explictly triggering it.

        Initial Comments:
        • On roadmap for TEF (but probably in H2' 24)
        • To be check by DT
        • For Orange, Ludovic will confirm but up to his knowledge a specific entity (product order) is managed for ordering a service with recurring payment. This productOrder is send from merchant to Carrier Billing server. Then payment are triggered from the merchant to the Carrier billing server depending on the periodicity. In the payment the product order is provided as reference.

        **Zoom in Reversal** by Mohamed (STC) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115). Relevant information indicated:
        • From a business flow side very similar to refund. In this case, paymentId is mandatory. It is proposed due to any problem in merchant/Operator side while performing a given payment
        • But very different behavior: It will not be reflected in the invoice and distinct behavior for fee/commission as well as they could be cancelled in this case.

        Next actions commented:
        • Operators to check priorities in order to drive technical work
        • Operators to provide Use Cases within the related issues for better understanding of them. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 10th-January 16:00 - 17:00 (CET)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..06035c3fa859fff3af500ad6a42345a3a29c9ff9 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10/raw.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 10-January-2024
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Pedro indicates he cannot attend the issue yet. He is going to generate local branch to perform the configurations as per [camaraproject/Commonalities#110](https://github.com/camaraproject/Commonalities/pull/110). Rafał explains that he has already applied in Device Status WG and identified some issues so far. The WoW is by generating a fork of the repository an testing in the fork as per the manual provided in the PR. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | After merging of second the [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) regarding Carrier Billing Enhancements, this issue is to settle this version as v0.2 Release Candidate. If no comments, the related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) will be merged at the end of this week (12th January). Orange has given their approval. After that, new Issue and PR will be generated for Release Generation. +New Carrier Billing Features | Track for new functionalities:
        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

        Priorities from the community:
        • For DT, it is needed to check with product team
        • For Orange, it is needed to check with product team
        • For STC, it is needed to check with product team
        • For Telefonica, it is refund
        • For Ericsson, as per their experience, it is refund

        Next actions commented:
        • Operators to check priorities in order to drive technical work. Kind reminder will be indicated within the related issues.
        • Operators to provide Use Cases within the related issues for better understanding of them. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 24th-January 16:00 - 17:00 (CET)
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7a532b5cc0e368302d07887d52b8c954b3462e33 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24/raw.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 24-January-2024
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Pedro has performed some progress on this. Thank you very much to Rafał's support on this. Using a fork-based approach linter has been tested. Details in [Testing_linter](https://github.com/PedroDiez/CarrierBillingCheckOut/pull/1). Some errors found in API Spec format to be reviewed and corrected prior to generate the Release. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Issue to track the generation of release v0.2.0. Related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) ongoing. Linting output to be applied before approving it and be ready to merge. +New Carrier Billing Features | Track for new functionalities:
        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

        Priorities from the community:
        • For DT, so far it is not settle special focus on this API, so as any way forward is seen OK
        • For Orange, it is needed to check with product team
        • For STC, it is refund (full/partial) as commented in related issue
        • For Telefonica, it is refund
        • For Ericsson, as per their experience, it is refund

        Next actions: Have a checkpoint in the next meeting. +AoB | Ludovic commented offline to Pedro that he is having internal meeting in the same slot until MWC. Commented in slack WG channel to check other options for meetings on 7th and 21th February respectively. Based on that new dates will be provided + + +### Next Steps +- Next Meetings:
        + • Next meeting: 7th February, 11:00 - 12:00 CET
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1e9fa5cc308153e3a27d6dc588a1c60b0844d739 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07/raw.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-February-2024
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Aziz Abouchi (SFR) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Telefonica | Release v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Currently focus in two main topics:
        • **Initial Release**: In final steps to deliver initial release (version v0.2.0).
        • **Linter rules**: Progressing well just to check final input from Commonalities PR#110. +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Using a fork-based approach, linter has been tested. Details in [Testing_linter](https://github.com/PedroDiez/CarrierBillingCheckOut/pull/1). Progressing very well in this track with the support of Rafał. Just pending to perform final tests based on latest status of Commonalities PR#110. Maybe some additional PR required to fix API Specification format prior to deliver initial release. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Issue to track the generation of release v0.2.0 - `CLOSED`. Related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) `MERGED`. +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Issue to generate Release v0.2.0 - `CLOSED`. Related PRs [PR#134](https://github.com/camaraproject/CarrierBillingCheckOut/pull/134) and [PR#137](https://github.com/camaraproject/CarrierBillingCheckOut/pull/137) `MERGED`. Pending to check output from Linter and maybe some additional PR required. +New Carrier Billing Features | Track for new functionalities:
        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

        Priorities from the community:
        • For DT, so far it is not settle special focus on this API, so as any way forward is seen OK
        • For Orange, need to check with product team whether refund or recurrent payments may have more priority. In any case it is OK with the move forward agreed
        • For STC, it is refund (full/partial) as commented in related issue
        • For Telefonica, it is refund
        • For Ericsson, as per their experience, it is refund

        Next actions: Let's begin discussion about refund and maybe we can work with recurrent payments in parallel after Orange's checking. +AoB | Aziz Abouchi (SFR) joints for the first time this WG. Context of the work made within the group explained to him. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 21th February, 16:00 - 17:00 CET
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7b48a9dcca2924d8c9444cbb60af79da9aa521a1 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21/raw.md @@ -0,0 +1,37 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-February-2024
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Telefonica | Release v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Initial Release**: Initial release delivered [Release v0.2.0](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.0).
        • **Linter rules**: Checked Successfully with configuration agreed in Commonalities. +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Issue to generate Release v0.2.0 - `CLOSED`. Related PRs [PR#134](https://github.com/camaraproject/CarrierBillingCheckOut/pull/134), [PR#137](https://github.com/camaraproject/CarrierBillingCheckOut/pull/137) and [PR#141](https://github.com/camaraproject/CarrierBillingCheckOut/pull/141) `MERGED`. +New Carrier Billing Features | Begin to work on Refund feature in next meetings. Requirements/User Stories to be compiled within Issue
        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104). +AoB |
        • **Linter Rules**: After checking successfully the configuration, new Issue/PR will be triggered to apply within the WG. AP@Pedro Diez.
        • **Release v0.2.0**: Checking internally API Publication in TEF, it has been advised that callback notifications endpoints has the same operationId "paymentNotification" for 1-STEP and 2-STEP generating some problems, so as different name will be given in order to avoid publication topics. This is not functional topic but a format one, so it will be managed as a fix. AP @Pedro Diez to open New Issue and related PR to generate a Fix on the release (v0.2.1). + + + +### Next Steps +- Next Meetings:
        + • Next meeting: 06th March, 16:00 - 17:00 CET
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8f4a5220b65386eb717cf57b874e7514f8332347 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06/raw.md @@ -0,0 +1,40 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-March-2024
        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[PR#142](https://github.com/camaraproject/CarrierBillingCheckOut/pull/142) | Telefonica | Update CHANGELOG +[PR#145](https://github.com/camaraproject/CarrierBillingCheckOut/pull/145) | Telefonica | Release v0.2.1 +[PR#146](https://github.com/camaraproject/CarrierBillingCheckOut/pull/146) | Telefonica | fix_changelog_redoc_link +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Initial Release**: Fix over initial release delivered [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1). Functional Release covering 1-STEP and 2-STEP Payments.
        • **Linter rules**: Checked Successfully with configuration agreed in Commonalities with the support of DT (Rafał). Pending PR to apply to this WG repo. **AP@Pedro Diez**. +[PR#142](https://github.com/camaraproject/CarrierBillingCheckOut/pull/142) | After generation of Release v0.2.0 minor Changelog fix is detected. Approved and `MERGED`. +[PR#145](https://github.com/camaraproject/CarrierBillingCheckOut/pull/145) | Generation of [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1) as a fix managing the fact the two callback endpoints were named with the same `operationId` and this may create publication and code generators issues. Approved and `MERGED`. +[PR#146](https://github.com/camaraproject/CarrierBillingCheckOut/pull/146) | After merging of Release v0.2.1 a minor fix in a API specification link identified. Approved and `MERGED` on 6th March, completing the work for [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1). +New Carrier Billing Features | Next Feature to work on:
        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
        • Requirements/User Stories to be compiled within Issue. Telefonica (Pedro) indicates final Business requirements have being received during this week and are under evaluation, commenting in advance full/partial refunds are requested. Main points will be reflected within the Issue. Also Ericsson (Ajit) indicates the support of full/partial refunds as a MUST. Objective is to compile requirements within the issue and begin to discuss in the next meeting the requirements and hopefully a draft proposal

        Orange (Ludovic) is pending checking priority from Business. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 20th March, 16:00 - 17:00 CET
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..034770ba27739c6febbbcc6d22df2a56ab0dc4e9 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20/raw.md @@ -0,0 +1,34 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 20-March-2024
        +**Status:** FINAL + +## Attendees + +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#148](https://github.com/camaraproject/CarrierBillingCheckOut/issues/148) | WG | Apply Linter Configuration in Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | WG | Refund functionality for Payment requests enhancement + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Linter rules**: Applied in WG.
        • Begin work about refunds +[Issue#148](https://github.com/camaraproject/CarrierBillingCheckOut/issues/148) | Issue opened to apply Linter rules in Carrier Billing WG repository, set to `CLOSED`. Related [PR#149](https://github.com/camaraproject/CarrierBillingCheckOut/pull/149) approved and `MERGED`. +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | Telefónica comments about the main requirements requested by their business and compiled within the Issue. Also commented during the meeting and include later the requirement of obtaining the balance of a given payment (which amount is not refunded). Some comments and considerations provided by Orange (Ludovic):
        • From Business perspective flow is delegated in Payment Aggregators with deals with the specific details of a given market and latter request in a homogeneous way to the Operator.
        • Even some Operators (e.g. Telefonica case) the amount refunded cannot exceed payment amount, we should not impose that as a general rule for any implementation as it may be business cases where for customer inconveniences, the amount refunded could be higher (e.g. to enforce trustability / fidelization from the customer).
        • With regards to asynchronism, it is asked whether refers to a 2-STEP procedure like payments. It is clarified that not related to a 2-STEP process but to design the solution to work with notifications as refund procedure could take some time before being committed.
        • Regarding API design, Orange comments about other option to model endpoint(s) in a way refering to the payment involved in the path: `/payments/{paymentId}/refunds`. + + +### Next Steps +- Next Meetings:
        + • Next meeting: 3rd April, 16:00 - 17:00 CET
        diff --git a/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/README/raw.md b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cbdccf6298314db6652fdb922dc4d1027f53ac8f --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since 3rd April WG Meeting, meeting minutes are placed in [CAMARA Carrier Billing WG Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/sp-cbc+Meeting+Minutes) diff --git a/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction/raw.md b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3b5bbf45b6741c34be16567614d2f2d644641f7a --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction/raw.md @@ -0,0 +1,33 @@ + + +# Document objective + +The following document provide a quick introduction of the Orange contribution for a Carrier Billing API + +# Use Case Definition + +The API swagger proposal covers sequence diagram illustrated in supportingDocument folder + + + +Note: +The API allows to manage : + +- a one-step payment (the request is a request to 'execute' a payment) or +- a 2-steps payment - in this case the first step is a payment preparation request that must be later conformed in order to be 'executed. It is possible to cancel a payment preparation. +- retrieve payment by id +- search payment from criterias + + +# API definition + +The proposed API did not features 'purchase' resource management. The purchase could be handeld separatly in another API +The purchase id could be referred in the payment (via referenceCode or via an explicit attribute to be added). + +In order to keep consistence with operator existing assets, the API resource model is directly design from standard RESTful Network API for Payment from the Open Mobile Alliance. + +# API open points + +- use of an explicit attribute to identify the msisdn 'to be charged' (to put right, to identyfy the account which must be charged. This account is identified via the msisdn linked to the account). +- The API could be simplified (for example remove resourceURL, serverReferenceode, etc...atributes if not relevant for our UC) +- Payment lifecyle must be disccussed - OMA could be used as proposal and simplified diff --git a/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/README/raw.md b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..220f01caa5a015a6cfd54e60ac74769669ec4546 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout/raw.md b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d513bd12130f2ee6e59faf44df25eafd5e67c49d --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout/raw.md @@ -0,0 +1,1066 @@ +# carrier_billing_checkout + +```yaml +openapi: 3.0.3 +info: + title: Carrier Billing Checkout + description: |- + Service that provides functionality for enabling the purchase and payment of goods against OB carrier billing systems. + + # Relevant Definitions and concepts + + - **Purchase**: The action of acquiring a good, service or product. + - **Payment**: The act or process of paying for that good, service or product. + - **Payable**: The concept, service or good a client is paying for. + + # API functionality + + This API allows to create and pay purchases of several Payables. Initial scope is focused in the purchase of digital goods via OB carrier billing systems. + + # Resources and Operations overview + + There are 2 resources in the API: + - The first one, **Purchases**, exposes two operations that allow to create and retrieve purchase info for a specific user. The unique supported **payable** so far is: + - **Digital Good:** Good that the user will acquire, provided by a third party (not the OB) (e.g.: purchase "extra" credit in online gaming, transport tickets, etc). + + - **Payments** is the second one and it exposes four operations to **request the payment** of a specific purchase via OB carrier billing systems **in one-step** (payment request) **or two-step** (payment preparation, payment confirmation or payment cancellation): + - **Carrier Billing:** It means that the operator will perform the billing, accordingly to the user's configuration in the OB; usually this implies that the purchase will be included in the user invoice and then charged to the user, but actually other options may eventually happen, like charge against user prepay balance or other. Notice that this option do not explicitly define the actual payment method, but means that the carrier will be doing the charge based on configuration out of scope of this API. + + - The last resource is **Purchase Notifications**. This resource has one operation to send events to the `notification_url`, when provided by the API client in the purchase creation. + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-write + - carrier-billing-checkout-purchase-digital-good-user-read + - carrier-billing-checkout-payment-user-write + - carrier-billing-checkout-user-notifications +servers: + - url: "{apiRoot}/{basePath}" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: carrier-billing-checkout/v0 + description: Base path for the Carrier Billing Checkout API +paths: + /purchases: + post: + tags: + - Purchases + summary: Creates a new purchase + description: Creates a new Purchase for a given payable + operationId: createPurchase + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Creates a new purchase + content: + application/json: + schema: + $ref: "#/components/schemas/CreatePurchase" + required: true + callbacks: + notifications: + "{$request.body#/notificationUrl}/notifications": + $ref: "#/paths/~1notifications" + responses: + "201": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Purchase created + content: + application/json: + schema: + $ref: "#/components/schemas/PurchaseCreated" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + RegulationTransactionAmountOverpassed: + summary: Purchase amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PURCHASE_AMOUNT_OVERPASSED + message: "Purchase amount overpasses applicable regulation" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + get: + tags: + - Purchases + summary: Retrieve a list of purchases + description: Obtain the list of purchases performed. If no pagination is indicated, list of purchases performed in the last 24 hours are returned. + operationId: getPurchases + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-read + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/Page' + - $ref: '#/components/parameters/PerPage' + - $ref: '#/components/parameters/Seek' + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Content-Last-Key: + $ref: '#/components/headers/Content-Last-Key' + X-Total-Count: + $ref: '#/components/headers/X-Total-Count' + description: Contains information about a list of purchases + content: + application/json: + schema: + $ref: "#/components/schemas/Purchases" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}: + get: + tags: + - Purchases + summary: Retrieve Purchase Information + description: Get Purchase Information of a given payable + operationId: getPurchaseInfo + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-read + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Contains information about a given purchase + content: + application/json: + schema: + $ref: "#/components/schemas/PurchaseInfo" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment: + post: + tags: + - Payments + summary: Creates a new Payment for a given payable in one-step + description: Creates a new Payment Procedure for a given payable. Once this operation is successful, payment process is triggered and no further action is required, that is, no other payment attempt must be done over the same purchaseId (error code 409 will be triggered). In case a payment attempt over a specific purchaseId ends with error, a new one attempt is allowed with the same conditions. + operationId: createPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + requestBody: + description: Request a new Payment + content: + application/json: + schema: + $ref: "#/components/schemas/RequestPayment" + required: true + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Performed + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + PhoneNumberRequired: + summary: Phone Number not provided and cannot be obtained from Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PHONE_NUMBER_REQUIRED + message: "Phone Number is required" + PhoneNumberMismatch: + summary: Phone Number provided not matching Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.INVALID_TOKEN_CONTEXT + message: "Phone Number does not match with Authorization context" + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/prepare: + post: + tags: + - Payments + summary: Creates a new Payment for a given payable in two-step + description: Creates a new Payment Procedure for a given payable. Once this operation is successful, payment process is reserved but not completely triggered/fulfilled. A second explicit action is required to confirm or cancel the payment. + operationId: preparePayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + requestBody: + description: Request a new Payment + content: + application/json: + schema: + $ref: "#/components/schemas/RequestPayment" + required: true + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Triggered + content: + application/json: + schema: + $ref: "#/components/schemas/PreparePaymentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + PhoneNumberRequired: + summary: Phone Number not provided and cannot be obtained from Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PHONE_NUMBER_REQUIRED + message: "Phone Number is required" + PhoneNumberMismatch: + summary: Phone Number provided not matching Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.INVALID_TOKEN_CONTEXT + message: "Phone Number does not match with Authorization context" + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/confirm: + post: + tags: + - Payments + summary: Confirm a Payment + description: Confirms a Payment for a given payable + operationId: confirmPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "202": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Accepted + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic409: + summary: Conflict + value: + status: 409 + code: ALREADY_EXISTS + message: "Another payment confirmation or cancellation has been triggered for the same purchase" + PaymentAlreadyReachedFinalStatus: + summary: Payment already reached a final status for the purchase + value: + status: 409 + code: CARRIER_BILLING_CHECKOUT.PAYMENT_REACHED_FINAL_STATUS + message: "Payment already reached a final status. No further actions can be performed" + "412": + $ref: "#/components/responses/Generic412" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/cancel: + post: + tags: + - Payments + summary: Cancel a Payment + description: Cancels a Payment for a given payable + operationId: cancelPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "202": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Cancellation Accepted + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic409: + summary: Conflict + value: + status: 409 + code: ALREADY_EXISTS + message: "Another payment confirmation or cancellation has been triggered for the same purchase" + PaymentAlreadyReachedFinalStatus: + summary: Payment already reached a final status for the purchase + value: + status: 409 + code: CARRIER_BILLING_CHECKOUT.PAYMENT_REACHED_FINAL_STATUS + message: "Payment already reached a final status. No further actions can be performed" + "412": + $ref: "#/components/responses/Generic412" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /notifications: + post: + tags: + - Purchase Notifications + summary: "Purchase notifications" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Carrier Billing Checkout server will call this endpoint whenever any purchase related event occurs. + operationId: purchaseNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Creates a new purchase Notification + content: + application/json: + schema: + $ref: "#/components/schemas/Notification" + required: true + responses: + "204": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Successful notification + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + security: + - apiKey: [] +components: + securitySchemes: + three_legged: + type: oauth2 + flows: + authorizationCode: + authorizationUrl: https://auth.example.com/authorize + tokenUrl: https://auth.example.com/token + scopes: + carrier-billing-checkout-purchase-digital-good-user-write: create purchases + carrier-billing-checkout-purchase-digital-good-user-read: read purchases + carrier-billing-checkout-payment-user-write: make payments + carrier-billing-checkout-user-notifications: read notifications + apiKey: + type: apiKey + description: API key to authorize requests + name: apikey + in: query + schemas: + CreatePurchase: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + notificationAuthToken: + type: string + example: "18dfdf79-e29b-41d4-a716-446655440000" + description: Authentication token for callback API endpoint + - additionalProperties: false + PurchaseCreated: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - processing + - succeeded + - failed + - cancelled + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `processing` - ConfirmPayment has been successfully triggered + * `succeeded` - Purchase payment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + * `cancelled` - CancelPayment has been successfully accomplished + notificationAuthToken: + type: string + example: "18dfdf79-e29b-41d4-a716-446655440000" + description: Authentication token for callback API endpoint + required: + - id + - status + additionalProperties: false + PurchaseBase: + type: object + description: Basic Representation of a Purchase Context + properties: + payable: + $ref: '#/components/schemas/PolymorphicPayable' + notificationUrl: + type: string + pattern: '^https:\/\/.+$' + description: Callback URL where service is going to be notified about any event. The received body definition is indicated in _Purchase notifications_ endpoint. + example: https://notifications-service.com/purchases/ + required: + - payable + PolymorphicPayable: + type: object + description: Basic representation of a payable resource/entity. Please refer to the Model to see all possible instances of Payable + properties: + type: + type: string + description: Type of payable + required: + - type + discriminator: + propertyName: type + mapping: + digital_good: "#/components/schemas/DigitalGood" + oneOf: + - $ref: "#/components/schemas/DigitalGood" + DigitalGood: + description: Basic representation of a digital good, including the total sum of all amount of the items. + allOf: + - $ref: '#/components/schemas/PolymorphicPayable' + - $ref: '#/components/schemas/MerchantInfo' + example: + type: digital_good + order: + id: MarketOrder1 + items: + - name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + - name: MarketOrderItemName2 + amount: + value: 40 + currency: EUR + taxIncluded: true + totalAmount: + value: 65 + currency: EUR + taxIncluded: true + merchant: + id: MerchantId1 + name: MerchantName1 + fee: 15.45 + MerchantInfo: + type: object + description: Represents a collection of goods belonging to a external merchant/provider to be paid + properties: + merchant: + $ref: '#/components/schemas/MarketMerchant' + order: + $ref: '#/components/schemas/MarketOrder' + required: + - order + MarketMerchant: + type: object + description: Represents a merchant/provider from external market + properties: + id: + type: string + description: Unique identifier of the merchant + name: + type: string + description: Merchant description + fee: + type: number + format: float + description: Fee percentage for the merchant/provider + required: + - id + example: + id: MerchantId1 + name: MerchantName1 + fee: 15.45 + MarketOrder: + type: object + description: Represents an order from external market + properties: + id: + type: string + description: Unique identifier of the order on the merchant/provider external system. Only provided when relevant from the API client point of view. + items: + type: array + minItems: 1 + items: + $ref: '#/components/schemas/MarketOrderItem' + totalAmount: + $ref: '#/components/schemas/MoneyAmount' + required: + - items + - totalAmount + example: + id: MarketOrder1 + items: + - name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + - name: MarketOrderItemName2 + amount: + value: 40 + currency: EUR + taxIncluded: true + totalAmount: + value: 65 + currency: EUR + taxIncluded: true + MarketOrderItem: + type: object + description: A item from external merchant/provider to be paid during checkout + properties: + name: + type: string + description: Item description provided by external merchant + amount: + $ref: '#/components/schemas/MoneyAmount' + required: + - name + - amount + example: + name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + MoneyAmount: + type: object + description: Money amount + properties: + value: + type: number + format: float + multipleOf: 0.01 + description: Amount value + currency: + type: string + description: Currency code in which the amount is expressed. ISO 4217 + taxIncluded: + type: boolean + description: true if the amount includes government taxes + default: false + required: + - value + - currency + PurchaseId: + type: string + format: uuid + description: Unique Purchase identifier + PurchaseInfo: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - processing + - succeeded + - failed + - cancelled + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `processing` - ConfirmPayment has been successfully triggered + * `succeeded` - ConfirmPayment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + * `cancelled` - CancelPayment has been successfully accomplished + paymentCreationDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is created in server database. This is a technical information. Time-offset from UTC may be used to match local OB time. + paymentDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is effectively performed. This is a business information. Time-offset from UTC may be used to match local OB time. + required: + - id + - status + additionalProperties: false + Purchases: + type: array + items: + $ref: '#/components/schemas/PurchaseInfo' + RequestPayment: + type: object + description: Data Type to indicate in payment request, either 1-step or 2-step. + properties: + phoneNumber: + type: string + description: The MSISDN on which the payment will be performed, in E.164 with `+` format. If no indicated, MSISDN has to be obtained from authorization context (i.e. Authorization header), otherwise exception will be raised. + example: + phoneNumber: '+34699999999' + PaymentInfo: + type: object + description: Data Type to indicate payment information + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + description: | + * `succeeded` - Payment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + enum: + - succeeded + - failed + required: + - id + - status + PreparePaymentInfo: + type: object + description: Data Type to indicate prepare payment information + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - failed + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + paymentOtp: + $ref: '#/components/schemas/PaymentOtp' + required: + - id + - status + PaymentOtp: + type: object + description: Data type to provide the necessary information in order to validate an OTP + properties: + validationEndpoint: + type: string + format: uri + description: URL for OTP validation + parameters: + type: object + description: Pairs of key/value for the parameters that have to be submitted as query parameters when calling the validation endpoint + required: + - validationEndpoint + Notification: + type: object + description: Data type with attributes required for generating a Purchase notification + properties: + purchaseId: + type: string + description: Unique Identifier of the purchase transaction + action: + type: string + enum: + - prepare_payment + - confirm_payment + - cancel_payment + description: | + Indication of the action notified by the event. + * `prepare_payment`: Notification about preparePayment procedure + * `confirm_payment`: Notification about confirmPayment procedure + * `cancel_payment`: Notificacion about cancelPayment procedure + status: + type: string + enum: + - succeeded + - failed + description: | + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + + NOTE: Under reception of a notification with failed status, new purchase procedure shall be initiated by API Client, if required. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + paymentDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is effectively performed. This is a business information. Time-offset from UTC may be used to match local OB time. + required: + - purchaseId + - action + - status + - description + ErrorInfo: + type: object + required: + - code + - message + - status + properties: + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + status: + type: integer + description: HTTP response status code + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + Seek: + name: seek + in: query + description: Index of last result read to create the next/previous number of results. This query parameter is used for pagination in systems with more than 1000 records + schema: + type: integer + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Indicates the total number of items in the collection (i.e. total purchases performed) + schema: + type: integer + responses: + Generic400: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_ARGUMENT + message: "Schema validation failed at ..." + Generic401: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Unauthorized + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: UNAUTHORIZED + message: "Authorization failed: ..." + Generic403: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + Generic404: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Resource Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: "The specified resource is not found" + Generic409: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: ALREADY_EXISTS + message: "A specified resource duplicate entry found" + Generic412: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Request cannot be executed in the current system state + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 412 + code: FAILED_PRECONDITION + message: "Request cannot be executed in the current system state" + Generic500: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: "Server error" + Generic503: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Service unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: SERVICE_UNAVALIBLE + message: "Service unavailable" + Generic504: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Request timeout exceeded + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: "Request timeout exceeded" +``` diff --git a/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment/raw.md b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..995fd7b8c8b1f9869767abf46bb1385cd8428487 --- /dev/null +++ b/marked/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment/raw.md @@ -0,0 +1,1020 @@ +# carrier_billing_payment + +```yaml +openapi: 3.0.3 +info: + description: Service Enabling Payments against OB Carrier Billing Systems + version: 0.7.0 + title: Carrier Billing Payment + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +servers: + - url: "{apiRoot}/{basePath}" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: payment/v0 + description: Base path for the carrier billing payment API +paths: + /payments: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - create-payment + tags: + - one-step-payment + summary: Create a new payment for subsequent charging to an end user’s bill + operationId: createPayment + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: '#/components/schemas/CreatePayment' + required: true + responses: + 201: + description: Created + content: + application/json: + schema: + $ref: '#/components/schemas/Payment' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + wrongCurrency: + summary: Currency is unknown or not authorized + value: + code: INVALID_INPUT + status: 400 + message: "Currency is unknown or not authorized: currency" + duplicateClientCorrelator: + summary: clientCorrelator still exist + value: + code: INVALID_INPUT + status: 400 + message: "clientCorrelator already exist on server" + unauthorizedAmount: + summary: unauthorized amount requested + value: + code: INVALID_INPUT + status: 400 + message: "unauthorized amount requested" + 401: + description: Unauthorized + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 403: + description: Forbidden + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 409: + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 500: + description: ServerError + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 503: + description: Service unavailable + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + get: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - list-payment + tags: + - payment + summary: retrieve payment(s) for subsequent charging to an end user’s bill + operationId: retrievePaymentList + description: retrieve payements based on criteria filtering. + parameters: + - $ref: '#/components/parameters/Fields' + - $ref: '#/components/parameters/Offset' + - $ref: '#/components/parameters/Limit' + responses: + 200: + description: OK + $ref: '#/components/responses/200PaymentArray' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + /payments/{paymentId}: + get: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - retrieve-payment + tags: + - payment + summary: retrieve a payment for subsequent charging to an end user’s bill + operationId: retrievePayment + description: retrieve payement formation for a given payment. + parameters: + - name: paymentId + in: path + description: Payment identifier that was obtained from the create payment operation + required: true + schema: + type: string + responses: + 200: + description: OK + content: + application/json: + schema: + $ref: '#/components/schemas/Payment' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 404: + $ref: "#/components/responses/Generic404" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + 503: + $ref: "#/components/responses/Generic503" + /payments/prepare: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - prepare-payment + tags: + - two-steps-payment + summary: Prepare a new payment procedure for subsequent charging to an end user’s bill + operationId: prepare + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: '#/components/schemas/BodyAmountReservationTransactionForReserveInput' + required: true + responses: + 201: + description: Created + content: + application/json: + schema: + $ref: '#/components/schemas/BodyAmountReservationTransactionForReserve' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + /payments/{paymentId}/confirm: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - confirm-payment + tags: + - two-steps-payment + summary: Confirm or Cancel a reservation on the user’s mobile account + operationId: confirmOrCancel + parameters: + - name: paymentId + in: path + description: The transaction identifier returned when the reservation was + created. + required: true + schema: + type: string + requestBody: + description: capture UnduserId for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/EndUserId" + required: true + responses: + 202: + description: Payment confirmation accepted + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + x-codegen-request-body-name: body + /payments/{paymentId}/cancel: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - cancel-payment + tags: + - two-steps-payment + summary: Cancel a payment preparation on the user’s mobile account + operationId: CancelPayment + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + required: true + schema: + type: string + requestBody: + description: capture UnduserId for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/EndUserId" + required: true + responses: + 202: + description: Payment Cancellation Accepted + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + x-codegen-request-body-name: body + /notifications: + post: + tags: + - Purchase notifications callback + summary: "Purchase notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Checkout server will call this endpoint whenever any purchase related event occurs. + operationId: purchaseNotification + requestBody: + description: Creates a new purchase Notification + content: + application/json: + schema: + $ref: "#/components/schemas/Notification" + required: true + responses: + "204": + description: Successful notification + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" +components: + schemas: + CreatePayment: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountTransactionInput' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + Payment: + required: + - amountTransaction + - paymentId + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + amountTransaction: + $ref: '#/components/schemas/AmountTransaction' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + paymentCreationDate: + type: string + description: Date when the payment is created in server data base. This is a technical information + format: date-time + paymentDate: + type: string + description: Date when the payment is effectively performed. This is a business information. + format: date-time + AmountTransaction: + required: + - endUserId + - paymentAmount + - referenceCode + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identifies the header that contains the external user token. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForCharge' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + AmountTransactionInput: + required: + - endUserId + - paymentAmount + - referenceCode + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForCharge' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + PaymentAmountForCharge: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + EndUserId: + required: + - endUserId + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided + BodyAmountReservationTransactionForReserve: + required: + - amountTransaction + - paymentId + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForReserve' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + BodyAmountReservationTransactionForReserveInput: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForReserveInput' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + AmountReservationTransactionForReserve: + required: + - endUserId + - paymentAmount + - referenceCode + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForReserve' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + AmountReservationTransactionForReserveInput: + required: + - endUserId + - paymentAmount + - referenceCode + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForReserve' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + PaymentAmountForReserve: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + BodyAmountReservationTransactionForConfirmOrCancel: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForConfirmOrCancel' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + BodyAmountReservationTransactionCancel: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForConfirmOrCancel' + AmountReservationTransactionForConfirmOrCancel: + required: + - endUserId + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForConfirmOrCancel' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + PaymentAmountForConfirmOrCancel: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + amountReserved: + type: number + description: Reserved amount. + totalAmountCharged: + type: number + description: Total amout charged. + ChargingInformation: + required: + - amount + - currency + - description + type: object + properties: + amount: + type: number + description: Amount to be charged or reserved. + currency: + type: string + description: Currency identifier as defined in [ISO4217]. + description: + type: string + description: Description text to be used for information and billing text + ChargingMetaData: + type: object + properties: + onBehalfOf: + type: string + description: Allows aggregators/partners to specify the actual payee. + purchaseCategoryCode: + type: string + description: Indication of the content type. + channel: + type: string + description: Billing policy + isTaxIncluded: + type: boolean + description: if true, the amount is tax included, if false the amount is provided without tax. In both cases, taxAmount could be valued to provide tax amount. + + taxAmount: + type: number + description: The tax amount charged by the merchant. This also provides an indicator to the downstream billing + system. + serviceId: + type: string + description: Billing ID + productId: + type: string + description: Product specification code + ErrorInfo: + type: object + required: + - code + - message + - status + properties: + code: + type: string + description: Code given to this error + status: + type: string + description: HTTP response status code + message: + type: string + description: Detailed error description + Notification: + type: object + description: Data type with attributes required for generating a Payment notification + properties: + paymentId: + type: string + description: Unique Identifier of the payment + action: + type: string + enum: + - prepare_payment + - confirm_payment + - cancel_payment + description: | + Indication of the action notified by the event. + * `prepare_payment`: Notification about preparePayment procedure + * `confirm_payment`: Notification about confirmPayment procedure + * `cancel_payment`: Notificacion about cancelPayment procedure + status: + type: string + enum: + - succeeded + - failed + description: | + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + NOTE: Under reception of a notification with failed status, new purchase procedure shall be initiated by API Client, if required. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + paymentDate: + type: string + description: Date when the payment is effectively performed. This is a business information. + format: date-time + required: + - paymentId + - action + - status + - description + responses: + Generic400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + Generic401: + description: Unauthorized + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: UNAUTHORIZED + status : 401 + message: "Authorization failed: ..." + Generic403: + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: FORBIDDEN + status: 403 + message: "Operation not allowed: ..." + Generic404: + description: Resource Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: NOT_FOUND + status : 404 + message: "The specified resource is not found" + Generic500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: SERVER_ERROR + status: 500 + message: "Server Error" + Generic503: + description: Service unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: SERVICE_UNAVAILABLE + status: 503 + message: "Service unavailable" + Generic504: + description: Request timeout exceeded + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: REQUEST_TIMEOUT_EXCEEDED + status: 504 + message: "Request timeout exceeded" + 200PaymentArray: + description: A list of payment(s) + headers: + X-Total-Count: + $ref: '#/components/headers/X-Total-Count' + X-Result-Count: + $ref: '#/components/headers/X-Result-Count' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/Payment' + parameters: + Fields: + name: fields + in: query + description: Comma-separated properties to be provided in response + schema: + type: string + Offset: + name: offset + in: query + description: Requested index for start of resources to be provided in response + schema: + type: integer + Limit: + name: limit + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + headers: + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer + X-Result-Count: + description: Actual number of items returned in the response body + schema: + type: integer + securitySchemes: + oAuth2ClientCredentials: + type: oauth2 + flows: + clientCredentials: + tokenUrl: '{tokenUrl}' + scopes: {} + BasicAuth: + type: http + scheme: basic + apiKey: + type: apiKey + description: API key to authorize requests + name: apikey + in: query + three_legged: + type: oauth2 + flows: + authorizationCode: + authorizationUrl: https://auth.example.com/authorize + tokenUrl: https://auth.example.com/token + scopes: + payment: perform payment +``` diff --git a/marked/ClickToDial/README/raw.md b/marked/ClickToDial/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c592a424cdc32814efac63744b64815f6f02a1d6 --- /dev/null +++ b/marked/ClickToDial/README/raw.md @@ -0,0 +1,49 @@ +
        + + + + + + + + +# ClickToDial + +Sandbox API Repository to describe, develop, document, and test the ClickToDial Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [Click To Dial](https://lf-camaraproject.atlassian.net/wiki/x/3DHe) + +## Scope +* Service APIs for “Click-To-Dial” +* It provides the API consumer with the ability to: + * establish a voice call between a caller and callee + * terminate an active call + * retrieve the recording of a call (if available) +* Describe, develop, document and test the APIs +* Started: September 2023 + + + + +## Release Information + +> [!NOTE] +> This repository has only pre-release versions available yet. Pre-releases are for testing and may change before public release. + +* The latest pre-release is [r1.2](https://github.com/camaraproject/ClickToDial/releases/tag/r1.2) (release candidate), with the following API versions: + * **click-to-dial 0.1.0-rc.1** + [[YAML]](https://github.com/camaraproject/ClickToDial/blob/r1.2/code/API_definitions/click-to-dial.yaml) [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ClickToDial/r1.2/code/API_definitions/click-to-dial.yaml&nocors) [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ClickToDial/r1.2/code/API_definitions/click-to-dial.yaml) + +* For changes see [CHANGELOG](https://github.com/camaraproject/ClickToDial/tree/main/CHANGELOG) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly (odd weeks), Wednesday, 3 PM CET/CEST (13:00 UTC,21:00 Beijing) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96843390032?password=1153dd0f-f8c8-4d3b-9962-d9685444d145) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/ClickToDial) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ClickToDial/code/API_definitions/click-to-dial/raw.md b/marked/ClickToDial/code/API_definitions/click-to-dial/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..911de2ec938fb6fed78c932930b72fa58111984b --- /dev/null +++ b/marked/ClickToDial/code/API_definitions/click-to-dial/raw.md @@ -0,0 +1,752 @@ +# click-to-dial + +```yaml +openapi: 3.0.3 + +info: + title: Click to Dial Service + description: | + The Click to Dial API allows API consumers to initiate and manage voice calls between two parties. The API processes call requests, sets up the call, and provides optional status notifications and call recording features. For specific details, please refer to [click-to-dial_API.md](/documentation/API_documentation/click-to-dial_API.md) + + # API functionality + + Based on the Click-to-Dial API, users can initiate and terminate click-to-call sessions. The Click-to-Call API has the following features: + + * The API consumer calls `POST /calls` to establish a call between the caller and the callee. + * The API consumer calls `DELETE /calls/{callId}` to terminate an active call session. + * Optionally, the API consumer can provide a callback URL (`sink`) to receive status notifications. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: "0.7" + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ClickToDial + +servers: + - url: '{apiRoot}/click-to-dial/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /calls: + post: + tags: + - Calls + summary: Create a new Click to Dial call session + description: | + Creates a new Click to Dial call session between the caller and the callee. + operationId: createCall + security: + - openId: + - "click-to-dial:calls:create" + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Create a Click to Dial call session. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallRequest' + responses: + '201': + description: Call created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Call" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '409': + $ref: '#/components/responses/Conflict409' + '422': + $ref: '#/components/responses/UnprocessableEntity422' + callbacks: + callStatusChanged: + '{$request.body#/sink}': + post: + summary: Call status changed event + description: | + Event notification delivered to the sink URL when the call status + changes (CloudEvents structured mode). + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/EventCTDStatusChanged' + examples: + CALL_STATUS_CHANGED_EXAMPLE: + $ref: '#/components/examples/CALL_STATUS_CHANGED_EXAMPLE' + responses: + '2XX': + description: Event successfully received by the sink. + /calls/{callId}: + get: + tags: + - Calls + summary: Get call details + description: Retrieve the details and current status of a Click to Dial call session. + operationId: getCall + security: + - openId: + - "click-to-dial:calls:read" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Call details + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Call" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + + delete: + tags: + - Calls + summary: Terminate an active call + description: | + Terminates an active Click to Dial call session identified by the given callId. + operationId: terminateCall + security: + - openId: + - "click-to-dial:calls:delete" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Call terminated + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '409': + $ref: '#/components/responses/Conflict409' + + /calls/{callId}/recording: + get: + tags: + - Recording + summary: Get call recording + description: Retrieve the recording associated with the given callId. + operationId: getRecording + security: + - openId: + - "click-to-dial:recordings:read" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Call recording resource + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RecordingResource" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + +components: + securitySchemes: + openId: + type: openIdConnect + description: This API uses OpenID Connect for authentication and authorization. + openIdConnectUrl: "https://example.com/.well-known/openid-configuration" + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: '#/components/schemas/XCorrelator' + example: 'b4333c46-49c0-4f62-80d7-f0ef930f1c46' + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for the different services + schema: + $ref: '#/components/schemas/XCorrelator' + example: 'b4333c46-49c0-4f62-80d7-f0ef930f1c46' + + schemas: + XCorrelator: + type: string + pattern: '^[a-zA-Z0-9-_:;./<>{}]{0,256}$' + description: Correlation id for tracking API calls across systems. + + callId: + description: Call identification + type: string + example: 'call_550e8400-e29b-41d4-a716-446655440000' + + Call: + description: Click to Dial call session resource + type: object + properties: + callId: + $ref: '#/components/schemas/callId' + caller: + $ref: '#/components/schemas/Caller' + callee: + $ref: '#/components/schemas/Callee' + status: + $ref: '#/components/schemas/status' + createdAt: + type: string + format: date-time + description: > + Time when the call session was created. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + recordingEnabled: + type: boolean + description: Whether recording is enabled for this call. + required: + - callId + - caller + - callee + - status + - createdAt + + CreateCallRequest: + description: Request to create a new Click to Dial call session + type: object + properties: + caller: + $ref: '#/components/schemas/Caller' + callee: + $ref: '#/components/schemas/Callee' + sink: + $ref: '#/components/schemas/sink' + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + recordingEnabled: + type: boolean + description: Whether call recording is enabled. + required: + - caller + - callee + example: + caller: + number: "+441234567890" + callee: + number: "+441234567891" + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "ya29.A0AR...exampletoken" + accessTokenExpiresUtc: "2026-01-01T00:00:00Z" + accessTokenType: bearer + recordingEnabled: true + + Caller: + type: object + properties: + number: + $ref: '#/components/schemas/PhoneNumber' + required: + - number + + Callee: + type: object + properties: + number: + $ref: '#/components/schemas/PhoneNumber' + required: + - number + + PhoneNumber: + description: Phone number in E.164 format + type: string + pattern: '^\+[1-9]\d{1,14}$' + example: '+12345678' + + sink: + description: The address to which events shall be delivered, using the HTTP protocol. + type: string + format: uri + example: "https://endpoint.example.com/sink" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + description: "The type of the credential. MUST be set to ACCESSTOKEN. Discriminator for credential subtypes." + type: string + enum: + - ACCESSTOKEN + discriminator: + propertyName: credentialType + mapping: + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + required: + - credentialType + + AccessTokenCredential: + description: An access token credential. + type: object + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + credentialType: + description: MUST be `ACCESSTOKEN` for this concrete credential schema. + type: string + enum: + - ACCESSTOKEN + example: ACCESSTOKEN + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: > + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - credentialType + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RecordingResource: + description: Recording file for a Click to Dial call + type: object + properties: + callId: + $ref: '#/components/schemas/callId' + content: + type: string + description: Base64 encoded audio content. + contentType: + type: string + description: MIME type of the audio file. + enum: + - audio/wav + - audio/mp3 + - audio/mpeg + - audio/ogg + generatedAt: + type: string + format: date-time + description: > + Timestamp when the recording was generated. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + required: + - callId + - content + - contentType + + EventCTDStatusChanged: + description: Common attributes of Click to Dial + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + properties: + callId: + $ref: '#/components/schemas/callId' + caller: + $ref: '#/components/schemas/PhoneNumber' + callee: + $ref: '#/components/schemas/PhoneNumber' + status: + type: object + description: | + Call status object. `state` contains the current lifecycle state + and `reason` contains an optional disconnection reason when applicable. + properties: + state: + $ref: '#/components/schemas/status' + reason: + $ref: '#/components/schemas/reason' + required: + - state + recordingResult: + $ref: '#/components/schemas/recordingResult' + callDuration: + $ref: '#/components/schemas/callDuration' + timestamp: + $ref: '#/components/schemas/timestamp' + required: + - callId + - caller + - callee + - status + - timestamp + required: + - data + + status: + description: Call status + type: string + enum: + - initiating + - callingCaller + - callingCallee + - connected + - disconnected + - failed + example: 'callingCaller' + + reason: + description: This field indicates the disconnection reason. This field is mandatory when status is 'disconnected'. + type: string + enum: + - hangUp + - callerBusy + - callerNoAnswer + - callerFailure + - callerAbandon + - calleeBusy + - calleeNoAnswer + - calleeFailure + - other + example: 'hangUp' + + recordingResult: + description: Recording Result. This field is mandatory when recording is enabled and the call is finished. + type: string + enum: + - success + - noRecord + - fail + example: 'success' + + callDuration: + description: This field indicates the duration of the calls, in seconds. This field is mandatory when status is 'disconnected'. + type: string + example: '1600' + + timestamp: + description: > + Time stamp, UTC time. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + type: string + format: date-time + example: '2017-12-04T18:07:57Z' + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: | + Event compliant with the CloudEvents specification. + Note: Providers MUST deliver events using CloudEvents structured mode + (HTTP header `Content-Type: application/cloudevents+json`). + type: object + properties: + id: + description: Identifier of this event, unique within the event `source` context. UUID is recommended. + type: string + format: uuid + example: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: + description: | + Identifies the context in which an event happened in the Provider implementation. + It SHOULD be an absolute URI identifying the producer (for example the API root or producer instance). + type: string + format: uri-reference + example: https://api.example.com/click-to-dial + type: + description: The type of the event. Use a vendor namespaced event type. + type: string + enum: + - "org.camaraproject.click-to-dial.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.click-to-dial.v0.status-changed: "#/components/schemas/EventCTDStatusChanged" + required: + - id + - source + - specversion + - type + - time + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific syntax exception used when a given field has a pre-defined range or an invalid filter criteria combination is requested. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated. + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + UnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + INVALID_PHONE_NUMBER: + value: + status: 422 + code: INVALID_PHONE_NUMBER + message: Caller or callee number is not a valid E.164 phone number. + SAME_CALLER_CALLEE: + value: + status: 422 + code: SAME_CALLER_CALLEE + message: Caller and callee cannot be the same number. + RECORDING_NOT_SUPPORTED: + value: + status: 422 + code: RECORDING_NOT_SUPPORTED + message: Recording is not supported for this call. + CALLER_NOT_AVAILABLE: + value: + status: 422 + code: CALLER_NOT_AVAILABLE + message: Caller number is currently not reachable or not allowed to start a call. + CALLEE_NOT_AVAILABLE: + value: + status: 422 + code: CALLEE_NOT_AVAILABLE + message: Callee number is currently not reachable or not allowed to receive a call. + + + Conflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + CALL_ALREADY_ACTIVE: + value: + status: 409 + code: CALL_ALREADY_ACTIVE + message: An active call already exists for the given caller and callee. + + examples: + CALL_STATUS_CHANGED_EXAMPLE: + description: | + Call status changed. This example shows a CloudEvent delivered in structured + mode (`Content-Type: application/cloudevents+json`). The `datacontenttype` describes + the `data` payload. + summary: Cloud event example for Click To Dial status change to disconnected due to hangUp + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: https://api.example.com/click-to-dial + specversion: "1.0" + datacontenttype: application/json + type: org.camaraproject.click-to-dial.v0.status-changed + time: 2021-12-12T00:00:00Z + data: + callId: "123e4567-e89b-12d3-a456-426614174000" + caller: "+12345678" + callee: "+12345678" + status: + state: "disconnected" + reason: "hangUp" + recordingResult: "success" + callDuration: "1600" + timestamp: "2017-12-04T18:07:57Z" +``` diff --git a/marked/ClickToDial/documentation/API_documentation/click-to-dial_API/raw.md b/marked/ClickToDial/documentation/API_documentation/click-to-dial_API/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c0462ec4bcbf9f4b80b017cad5fb66f3e48b964a --- /dev/null +++ b/marked/ClickToDial/documentation/API_documentation/click-to-dial_API/raw.md @@ -0,0 +1,321 @@ +# Overview + +The Click to Dial API allows API consumers to initiate and manage voice calls between two parties. The API processes call requests, sets up the call, and provides optional status notifications and call recording features. + +## 1. Introduction + +The Click to Dial API provides a standardized interface to initiate and manage voice call sessions between two parties. It allows API consumers to create a call session, retrieve call status and details, terminate an active call, and retrieve call recordings (if enabled). + + + +## 2\. Quick Start + +### 2.1 Prerequisites + +- **Authentication**: Obtain an OpenID Connect access token from your API provider. + + ```bash + curl -X POST "{openid_token_url}" -d "grant_type=client_credentials&client_id={your_id}&client_secret={your_secret}" + ``` + +### 2.2 Quick Try + +#### 2.2.1 Initiate a Call + +```bash +curl -X POST "{apiRoot}/calls" \ + -H "Authorization: Bearer {access_token}" \ + -H "Content-Type: application/json" \ + -d '{ + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "sink": "https://yourapp.example.com/clicktodialstatusnotify", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "{sink_access_token}", + "accessTokenExpiresUtc": "2025-12-31T23:59:59Z", + "accessTokenType": "bearer" + }, + "recordingEnabled": true + }' +``` + +- **Response:** + +```json +{ + "callId": "123e4567-e89b-12d3-a456-426614174000", + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "status": "initiating", + "createdAt": "2025-12-11T12:00:00Z", + "recordingEnabled": true +} +``` + +#### 2.2.2 Status Notification Callback + +- Implement an HTTP POST endpoint at your provided `sink` URL to receive status notifications. Example payloads are provided in the OpenAPI spec. + +#### 2.2.3 Release a Call + +```bash + curl -X DELETE "{apiRoot}/calls/{callId}" \ + -H "Authorization: Bearer {access_token}" \ +``` + +**Response:** +HTTP 204 No Content + +#### 2.2.4 Download Recording + +```bash +curl -X GET "{apiRoot}/calls/{callId}/recording" \ + -H "Authorization: Bearer {access_token}" \ +``` + +**Response:** + +```json +{ + "callId": "123e4567-e89b-12d3-a456-426614174000", + "content": "BASE64_ENCODED_AUDIO", + "contentType": "audio/wav", + "generatedAt": "2025-12-11T12:05:00Z" +} +``` + +### 2.3 Key Tips + +- **Number Format:** All phone numbers (caller, callee) must be in E.164 format, e.g., "+12345678". +- **Authentication:** Use OpenID Connect; include your access token as a Bearer token. +- **Status Codes:** 201 = created (POST /calls), 200 = success for reads, 204 = no content (DELETE /calls/{callId}), 400 = bad input, 401 = unauthorized, 403 = forbidden, 404 = not found, 409 = conflict, 422 = validation error. +- **Debugging:** Error responses include a code and description/message. + +## 3\. Authentication and Authorization + +This API uses **OpenID Connect** for authentication and authorization. Obtain your access token from your provider and use it in the Authorization header for all API requests. + +## 4\. API Documentation + +### 4.1 API Version + +wip + +### 4.2 Details + +#### 4.2.1 API sequencing + +1. Client calls **POST /calls** to start a call. +2. Server initiates calls to both caller and callee. +3. (Optional) Client may call **DELETE /calls/{callId}** to end a call. +4. Status notifications are sent via HTTP POST to the provided `sink` URL as CloudEvents (structured mode). + +#### 4.2.1 API attributes + +##### Click to Dial Initiation Request + +| Name | Description | Required | Example | +| -------------- | --------------------------------------------------- | -------- | ---------------------------- | +| caller | Calling party number (E.164, with "+") | Yes | "+12345678" | +| callee | Called party number (E.164, with "+") | Yes | "+87654321" | +| sink | (Optional) Callback URL for status notifications | No | `` | +| sinkCredential | (Optional) Callback authentication info (see below) | No | (see below) | + +##### sinkCredential (for `ACCESSTOKEN` type) + +The `SinkCredential` is a discriminator-based object. Currently the only supported `credentialType` is `ACCESSTOKEN` and the concrete `AccessTokenCredential` MUST include the fields below. + +| Name | Description | Required | Example | +| --------------------- | --------------------------------------------- | -------- | ---------------------- | +| credentialType | Must be `ACCESSTOKEN` (discriminator) | Yes | `ACCESSTOKEN` | +| accessToken | Access token used to authenticate event POSTs | Yes | `sink_token` | +| accessTokenExpiresUtc | UTC expiry timestamp for the access token | Yes | `2025-12-31T23:59:59Z` | +| accessTokenType | Token type (OAuth token type) | Yes | `bearer` | + +##### Click to Dial Status Notify (callback payload) + +Status notifications are delivered as CloudEvents (see CloudEvent section below). The `data` payload for `EventCTDStatusChanged` contains the following fields. Note that `status` is now an object containing `state` and optional `reason`. + +| Name | Description | Required | Notes/Values | +| --------------- | -------------------------------------------------------- | -------- | ----------------------------------------------------------------------------- | +| caller | Calling party number (E.164) | Yes | | +| callee | Called party number (E.164) | Yes | | +| status | Object with `state` (lifecycle) and optional `reason` | Yes | `state`: `initiating`,`callingCaller`,`callingCallee`,`connected`,`disconnected`,`failed` | +| status.reason | Disconnection reason (if `state` is `disconnected`) | Cond. | `hangUp`,`callerBusy`,`callerNoAnswer`,`callerFailure`,`callerAbandon`,`calleeBusy`,`calleeNoAnswer`,`calleeFailure`,`other` | +| recordingResult | Recording result when recording enabled | Cond. | `success`,`noRecord`,`fail` | +| callDuration | Duration in seconds (present when call ended) | Cond. | | +| timestamp | UTC timestamp of the event / state change | Yes | RFC 3339 format | +| callId | Identifier of the call (matches the `callId` returned) | Yes | UUID style string | + +#### Release Call + +- Call identifier is provided as a path parameter in DELETE `/calls/{callId}`. + +#### Recording Download + +- Call identifier as path parameter in GET `/calls/{callId}/recording`. + +### 4.3 Endpoint Definitions + +| Endpoint | Method | Description | +| ------------------------------------ | ------ | ---------------------------------- | +| /calls | POST | Start a click-to-dial call | +| /calls/{callId} | GET | Retrieve call details | +| /calls/{callId} | DELETE | End (release) a click-to-dial call | +| /calls/{callId}/recording | GET | Download call recording | + +### 4.4 Errors + +Errors follow the standard format: + +```json +{ + "status": 400, + "code": "INVALID_ARGUMENT", + "message": "Client specified an invalid argument, request body or query param." +} +``` + +Reference the [OpenAPI YAML](../../code/API_definitions/click-to-dial.yaml) for exact error codes and descriptions. + +#### 4.4.1 422 — Business error codes (Unprocessable Entity) + +When a request is syntactically correct but semantically invalid, the API returns `422 Unprocessable Entity` with a business `code` describing the error. The following 422 business error codes are defined in the OpenAPI spec: + +| Code | Description | +| ---- | ----------- | +| `INVALID_PHONE_NUMBER` | Caller or callee number is not a valid E.164 phone number. | +| `SAME_CALLER_CALLEE` | Caller and callee cannot be the same number. | +| `RECORDING_NOT_SUPPORTED` | Recording is not supported for this call. | +| `CALLER_NOT_AVAILABLE` | Caller number is currently not reachable or not allowed to start a call. | +| `CALLEE_NOT_AVAILABLE` | Callee number is currently not reachable or not allowed to receive a call. | + +Example 422 response: + +```json +{ + "status": 422, + "code": "INVALID_PHONE_NUMBER", + "message": "Caller or callee number is not a valid E.164 phone number." +} +``` + +Note: Additional common CAMARA error responses may be defined in the `CAMARA_common.yaml` referenced by this API's readiness checklist. Always consult the OpenAPI YAML for the authoritative list. + +## CloudEvent delivery notes + +- Providers MUST send status notifications as CloudEvents in structured mode. The HTTP header must be `Content-Type: application/cloudevents+json`. +- The CloudEvent MUST include the attributes: `id`, `source`, `type`, `specversion`, and `time`. +- The CloudEvent attribute `datacontenttype` MUST be `application/json` for the `data` payload. + +The CloudEvent `data` payload for Click-to-Dial `EventCTDStatusChanged` includes `callId`, `caller`, `callee`, `timestamp` and `status` (where `status` is an object with `state` and optional `reason`). Providers MUST set `datacontenttype` to `application/json`. + +Example CloudEvent (structured mode) — `CALL_STATUS_CHANGED_EXAMPLE` from the OpenAPI spec: + +```json +{ + "id": "83a0d986-0866-4f38-b8c0-fc65bfcda452", + "source": "https://api.example.com/click-to-dial", + + "specversion": "1.0", + "datacontenttype": "application/json", + "type": "org.camaraproject.click-to-dial.v0.status-changed", + "time": "2021-12-12T00:00:00Z", + "data": { + "callId": "123e4567-e89b-12d3-a456-426614174000", + "caller": "+12345678", + "callee": "+12345678", + "status": { + "state": "disconnected", + "reason": "hangUp" + }, + "recordingResult": "success", + "callDuration": "1600", + "timestamp": "2017-12-04T18:07:57Z" + } +} +``` + +Providers SHOULD ensure event `id` uniqueness and may retry delivery on transient failures. When delivering events to a `sink` that requires authentication, use the provided `sinkCredential` (e.g., set `Authorization: Bearer ` for `ACCESSTOKEN`). + +## Call flow (sequence diagram) + +The following sequence diagram shows the typical flow when creating a Click-to-Dial session, delivering events, and terminating the call. This is a logical flow; implementers may optimize or parallelise steps. + +```mermaid +sequenceDiagram + participant Client + participant Provider + participant Caller + participant Callee + participant Sink + + Client->>Provider: POST /calls {caller, callee, sink, sinkCredential} + Provider->>Caller: Place outbound call to caller + Provider->>Callee: Place outbound call to callee + Provider-->>Client: 201 Created {callId, status} + Provider->>Sink: CloudEvent (status: initiating) + Provider->>Sink: CloudEvent (status: connected) + Client->>Provider: DELETE /calls/{callId} + Provider->>Sink: CloudEvent (status: disconnected) +``` + + +### 4.5 Policies + +N/A + +### 4.6 Example Code Snippets + +#### Start a Call + +```bash +curl -X POST "{apiRoot}/calls" \ + -H "Authorization: Bearer {access_token}" \ + -H "Content-Type: application/json" \ + -d '{ + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "sink": "https://yourapp.example.com/clicktodialstatusnotify", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "{sink_access_token}", + "accessTokenExpiresUtc": "2025-12-31T23:59:59Z", + "accessTokenType": "bearer" + } + }' +``` + +#### Release a Call + +```bash +curl -X DELETE "{apiRoot}/calls/{callId}" \ + -H "Authorization: Bearer {access_token}" +``` + +#### Download a Recording + +```bash +curl -X GET "{apiRoot}/calls/{callId}/recording" \ + -H "Authorization: Bearer {access_token}" +``` + +### 4.7 FAQ's + +To be added in future versions. + +### 4.8 Terms + +N/A + +### 4.9 Release Notes + +This section lists release notes for historical versions. +The current version on the main branch is **wip**. + +- **0.1.0-alpha.1** — Initial release (archived). + +## References + +For a full API schema, see [code/API_definitions/click-to-dial.yaml](../../code/API_definitions/click-to-dial.yaml). diff --git a/marked/ClickToDial/documentation/API_documentation/click-to-dial_User_Story/raw.md b/marked/ClickToDial/documentation/API_documentation/click-to-dial_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f26e03ef48a66234f077fc4447bb2e5c42689b34 --- /dev/null +++ b/marked/ClickToDial/documentation/API_documentation/click-to-dial_User_Story/raw.md @@ -0,0 +1,65 @@ +# Click-to-Dial (CTD) API User Story + +| **Item** | **Details** | +| --------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **Summary** | As an application developer, I want to allow API consumers to initiate Click-to-Dial call sessions via the provider API so that two parties (caller and callee) can be connected via a voice call. The API should support call creation, termination, optional recording, and asynchronous status notifications. | +| **Roles, Actors and Scope** | **Roles:** API consumer; **Actors:** Application developers, integration engineers, CSP (service provider); **Scope:** Create and remove CTD session resources (calls), receive status notifications and retrieve recordings when available. | +| **Pre-conditions** | The client application has been onboarded and is authorized to call the API (has a valid access token with required scopes); the client knows the `apiRoot` and can send HTTP requests; if event delivery is required, the client provides a reachable `sink` URL and optional `sinkCredential`. | +| **Activities / Steps** | Start: Client calls `POST /calls` with `caller`, `callee` and optional `sink`/`sinkCredential`. Flow: Provider places calls to both parties and manages the session; Provider delivers status notifications as CloudEvents to the configured `sink`. End: Client calls `DELETE /calls/{callId}` or session ends normally (call disconnected). | +| **Post-conditions** | Call session resource exists with a `callId` and lifecycle `status`; if `sink` was provided, the provider sends CloudEvents (structured mode) to the `sink` with updates about call state changes; when recording is enabled and the call completes, a recording resource may be available at `GET /calls/{callId}/recording`. | +| **Exceptions** | Authentication/authorization failure (401/403); invalid request body or parameters (400/422); conflicting state when trying to terminate (409); event delivery failures to the `sink` (provider may retry or record failures). | + +## Key implementation details (aligning with API spec) + +- Endpoint naming and behaviour + + - `POST /calls` — create a new CTD call session. Success returns `201 Created` with a `Call` resource body containing `callId`, `caller`, `callee`, `status`, `createdAt`, etc. + - `DELETE /calls/{callId}` — terminate an active call. Returns `204 No Content` when successful. + - `GET /calls/{callId}` — retrieve call details. + - `GET /calls/{callId}/recording` — retrieve recording resource when available. +- Request and response shapes + + - The `CreateCallRequest` expects `caller` and `callee` objects (each with `number` in E.164 format). Optional `sink` (URI) and `sinkCredential` may be provided. Example: + +```json +{ + "caller": { "number": "+441234567890" }, + "callee": { "number": "+441234567891" }, + "sink": "https://example.com/sink", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "ya29.A0AR...", + "accessTokenExpiresUtc": "2026-01-01T00:00:00Z", + "accessTokenType": "bearer" + }, + "recordingEnabled": true +} +``` + +- `SinkCredential` and authentication + + - `SinkCredential` is a discriminator object. Currently the only supported `credentialType` is `ACCESSTOKEN` and the concrete `AccessTokenCredential` MUST include `accessToken`, `accessTokenExpiresUtc` and `accessTokenType`. + - When `sinkCredential` is provided, the provider will use the credential to authenticate HTTP requests to the `sink` when delivering events. The provider should set the `Authorization` header (e.g., `Authorization: Bearer `) when posting events. +- CloudEvents and notifications + + - Providers MUST deliver status notifications as CloudEvents in structured mode (`Content-Type: application/cloudevents+json`). + - The CloudEvent MUST include `id`, `source`, `type`, `specversion`, `time`, and `datacontenttype`. `datacontenttype` for our events is `application/json`. + - The event `data` payload for `EventCTDStatusChanged` contains `callId`, `caller`, `callee`, `timestamp` and `status` (an object): + +```json +"status": { + "state": "disconnected", + "reason": "hangUp" +} +``` + +- `status.state` values: `initiating`, `callingCaller`, `callingCallee`, `connected`, `disconnected`, `failed`. +- `status.reason` is present only when `status.state` is `disconnected` and must be one of the documented disconnection reasons. + +## Example end-to-end + +1. Client POSTs to `/calls` with `caller`, `callee`, optional `sink`/`sinkCredential`. +2. Provider returns `201 Created` with call details including `callId`. +3. Provider sends CloudEvents to `sink` as the call progresses with call status updates. +4. When the call ends, provider sends a final `disconnected` state event including `callDuration` and, if recording was enabled, `recordingResult`. +5. Client can `GET /calls/{callId}/recording` to download the recording resource if available. diff --git a/marked/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10/raw.md b/marked/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6da457ec5c52244aa531eed06bee6ac016927ef0 --- /dev/null +++ b/marked/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10/raw.md @@ -0,0 +1,35 @@ +# Click to Dial Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) + +* Hanbai Wang (China Mobile) + +* Yu Liu (China Mobile) + +* Shuting Qing (Huawei) + +* Jin Xu (Huawei) + + + +## Agenda +* Discuss the Bi-Weekly Meeting +* Past PR reviews +* Project Timeline + + + +## Discussion + +* The bi-weekly meeting will be scheduled for Friday afternoons every two weeks and will be strictly adhered to in the future. The meeting link will be the Teams connection on the homepage of the click-to-dial subproject team. The weekly meetings will need to discuss unresolved PRs and issues. + +* Firstly, it is clear that all PRs must be discussed in each meeting before they can be merged. After this meeting, the PR with formatting issues mentioned by Herbert needs to be revised and discussed in the next meeting. Only after the discussion and approval can it be merged. The md file format of the Click-to-Dial API user story has significant issues that need to be corrected promptly. The revised version must be discussed in the next meeting. + +* Regarding the project timeline, the current plan is to complete the user story, API definition, API YAML code, and other mandatory documents noted in the checklist by September. Additionally, a deliverable version should be identified. The testing of this API should be completed by the end of this year. + + + + + diff --git a/marked/ClickToDial/documentation/MeetingMinutes/README/raw.md b/marked/ClickToDial/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ClickToDial/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ClickToDial/documentation/SupportingDocuments/README/raw.md b/marked/ClickToDial/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ClickToDial/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConnectedNetworkType/README/raw.md b/marked/ConnectedNetworkType/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..546ab524e77107a06d619070dfae38f80c3c31f5 --- /dev/null +++ b/marked/ConnectedNetworkType/README/raw.md @@ -0,0 +1,60 @@ + + + + + + + + + +# ConnectedNetworkType + +Sandbox API Repository to describe, develop, document, and test the ConnectedNetworkType Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQD1Bg) + +## Scope + +* Service API(s) “ConnectedNetworkType” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * query the the mobile technology of the network that the device is connected to + * receive notifications when the connected network type has changed +* Describe, develop, document, and test the API(s) +* Started: June 2024 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ConnectedNetworkType/releases/tag/r1.2) (Fall25), with the following API versions: + * **connected-network-type-subscriptions v0.2.0** + [[YAML]](https://github.com/camaraproject/ConnectedNetworkType/blob/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml) + * **connected-network-type v0.2.0** + [[YAML]](https://github.com/camaraproject/ConnectedNetworkType/blob/r1.2/code/API_definitions/connected-network-type.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ConnectedNetworkType/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConnectedNetworkType/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ConnectedNetworkType/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions/raw.md b/marked/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..257295ae919c698d788f1752fbb060a06e461c94 --- /dev/null +++ b/marked/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions/raw.md @@ -0,0 +1,1719 @@ +# connected-network-type-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Connected Network Type Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to notifications on changes to the connected network type of a device. + + # Introduction + + ## Connected Network Type Subscription + API consumers can subscribe to receive notifications when the connected network type of a device changes. These notifications are delivered through CloudEvents. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Connected Network Type**: This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`: if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`: if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`: if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`: if device is connected to the 5G network technology + - `UNKNOWN`: if connection technology can not be determined + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type Subscription Management + + These endpoints allow you to manage subscriptions for receiving notifications on changes to the connected network type of a device. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed``: This event is triggered when the connected network type of the device changes. + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + When ``initialEvent`` is set to ``true`` in the subscription request, a notification has to be sent immediately to provide the connected network type of the device targeted. + Note: If the status can not be determined, or if the device is not connected, we send an initial event with ``connectedNetworkType`` valued to`UNKNOWN`. + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding connected network type can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which connected network type notifications should be generated. If the phone number is used as the device identifier when creating a subscription in a multi-SIM scenario, the API may: + - respond with an error, or + - generate network type change notifications for the multi-SIM group as a whole, or + - generate network type change notifications for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ConnectedNetworkType + +servers: + - url: "{apiRoot}/connected-network-type-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Connected Network Type Subscription + description: Operations to manage subscriptions for receiving notifications on changes to the connected network type of a device. + +paths: + /subscriptions: + post: + tags: + - Connected Network Type Subscription + summary: "Create a subscription for receiving notifications on changes to the connected network type of a device" + description: Create a subscription for receiving notifications on changes to the connected network type of a device. + operationId: createConnectedNetworkTypeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The connectivity network type status server will call this endpoint whenever the connected network type of the device changes. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + network-type-changed: + $ref: "#/components/examples/NETWORK_TYPE_CHANGED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created (Successful creation of subscription) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Identifier: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a list of device connected network type event subscription" + description: Retrieve a list of device connected network type event subscription(s) + operationId: retrieveConnectedNetworkTypeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a device connected network type event subscription for a device" + description: retrieve ConnectedNetworkType subscription information for a given subscription ID. + operationId: retrieveConnectedNetworkTypeSubscription + security: + - openId: + - connected-network-type-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Identifier: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connected Network Type Subscription + summary: "Delete connected network type event subscription for a device" + operationId: deleteConnectedNetworkTypeSubscription + description: delete a given ConnectedNetworkType subscription. + security: + - openId: + - connected-network-type-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: ConnectedNetworkType subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ConnectedNetworkType: + type: string + description: Network Type is intended to provide insight to connected network's capabilities from standards perspective. Actual network capabilities may differ based on implementation and MUST be checked with the connected network provider. + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes + subscription-started - Event triggered when the subscription starts + subscription-updated - Event triggered when the subscription is updated + subscription-ended - Event triggered when the subscription is terminated + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-started + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed: "#/components/schemas/EventNetworkTypeChange" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventNetworkTypeChange: + description: event structure for network type change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/EventNetworkTypeChangeData" + + EventNetworkTypeChangeData: + description: Event detail structure for network type changed data events + type: object + required: + - connectedNetworkType + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnded: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + SubscriptionEnded: + description: Event detail structure for SUBSCRIPTION_ENDED event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + NETWORK_TYPE_CHANGED: + description: The cloud event when a connected network type changed + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + specversion: "1.0" + datacontenttype: application/json + data: + subscriptionId: "987654321" + device: + phoneNumber: "+123456789" + connectedNetworkType: 5G + time: "2023-03-22T05:40:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a connected network type subscription ends + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended" + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ACTIVATION_REQUESTED: + description: Subscription details for a subscription whose activation has been requested + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + description: Subscription details for a subscription that has been deleted + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + SUBSCRIPTION_STARTED: + description: The cloud event when a connected network type subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.connected-network-type-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a connected network type subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + description: Subscription details for an active subscription + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + status: ACTIVE + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER: + description: Subscription details for an active subscription when a device identifier is also returned + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + status: ACTIVE + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + + CREATE_SUBSCRIPTION: + description: Subscription creation confirmation + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] +``` diff --git a/marked/ConnectedNetworkType/code/API_definitions/connected-network-type/raw.md b/marked/ConnectedNetworkType/code/API_definitions/connected-network-type/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c0bc813c20f97ca35e0482211ce05420cff666c4 --- /dev/null +++ b/marked/ConnectedNetworkType/code/API_definitions/connected-network-type/raw.md @@ -0,0 +1,529 @@ +# connected-network-type + +```yaml +openapi: 3.0.3 +info: + title: Connected Network Type + description: | + This API provides the customer with the ability to query to which Mobile Communication Technology it is connected to. + + # Introduction + + ## Connected Network Type + + The API consumer is able to query the device's connected network type. The API provider can determine this in various ways. For example, the network type can be inferred from the specific radio cell to which the device is connected, as radio cells only support a single technology. It is important to note that the API does not query the device directly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Connected Network Type** : This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`, if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`, if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`, if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`, if device is connected to the 5G network technology + - `UNKNOWN` if connection [technology] can not be determined + + * **LastStatusTime** : This property specifies the time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type + + The endpoint `POST /retrieve` allows to get connected Network Type. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which the connected network type should be returned. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a common connected network type for the multi-SIM group as a whole, or + - return the connected network type for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConnectedNetworkType + +servers: + - url: "{apiRoot}/connected-network-type/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Connected Network Type + description: Operations to get the network type device is connected to +paths: + /retrieve: + post: + tags: + - Connected Network Type + summary: "Get the connected network type" + description: Get the connected network type to which the user device is connected + operationId: getConnectedNetworkType + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - connected-network-type:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeRequest" + required: true + responses: + "200": + description: Contains connected network type + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeResponse" + examples: + Connected To 4G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected To 4G With Device Disambiguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected To 5G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 5G + Connectivity Unknown: + description: Device is not connected to its home mobile network. It may be connected to a different network (e.g. roaming or a WiFi network) or not connected at all. + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: UNKNOWN + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + LastStatusTime: + description: | + The last time that the connected network type status was confirmed to be correct by the API provider. The status should still be valid, but the API provider is unable to confirm this. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ConnectedNetworkTypeResponse: + type: object + required: + - lastStatusTime + - connectedNetworkType + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + + ConnectedNetworkType: + description: | + * UNKNOWN: Used when connection [technology] can not be determined + * 2G: 2nd Generation Mobile Communication Technology + * 3G: 3rd Generation Mobile Communication Technology + * 4G: 4th Generation Mobile Communication Technology + * 5G: 5th Generation Mobile Communication Technology + + type: string + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ConnectedNetworkTypeRequest: + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md b/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..12afc4cde5759507cd80cac7bcb2f4909705a0d8 --- /dev/null +++ b/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for connected-network-type 0.2.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type.yaml](/code/API_definitions/connected-network-type.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type.feature](/code/Test_definitions/connected-network-type.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/84FlBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md b/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e3064ecae34e7eb20420374340516291bf56a3a2 --- /dev/null +++ b/marked/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for connected-network-type-subscriptions 0.2.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type-subscriptions.yaml](/code/API_definitions/connected-network-type-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type-subscriptions.feature](/code/Test_definitions/connected-network-type-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/sYFmBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ConnectedNetworkType/documentation/SupportingDocuments/README/raw.md b/marked/ConnectedNetworkType/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConnectedNetworkType/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConnectivityInsights/README/raw.md b/marked/ConnectivityInsights/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a819f514ccde69e46738d51446acdd0e43938f73 --- /dev/null +++ b/marked/ConnectivityInsights/README/raw.md @@ -0,0 +1,59 @@ + + + + + + + + + +# ConnectivityInsights + +Sandbox API Repository to describe, develop, document, and test the ConnectivityInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KTLe) + +## Scope +* Service APIs for “Connectivity Insights” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * share key details about their applications that are relevant for network-related decisions across various CAMARA APIs. + * gain visibility into network quality, allowing them to +check if their application's network requirements can be met for a given user session. Based on the API’s response, developers can make informed decisions - like requesting a network boost through CAMARA Quality on Demand API or adjusting application settings (e.g. adjust video resolution) to ensure the best possible user experience. + * enables application developers to receive continuous updates +about network quality through event notifications. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: November 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/ConnectivityInsights/releases/tag/r3.2) (Fall25), with the following API versions: + * **connectivity-insights-subscriptions v0.6.0** + [[YAML]](https://github.com/camaraproject/ConnectivityInsights/blob/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml) + * **connectivity-insights v0.6.0** + [[YAML]](https://github.com/camaraproject/ConnectivityInsights/blob/r3.2/code/API_definitions/connectivity-insights.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ConnectivityInsights/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConnectivityInsights/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ConnectivityInsights/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Schedule: Bi-weekly on Wednesday at 1500UTC + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vTve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions/raw.md b/marked/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..24ae7639bd124f69c3beba9db8fdd1880cbff8d5 --- /dev/null +++ b/marked/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions/raw.md @@ -0,0 +1,1366 @@ +# connectivity-insights-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Connectivity Insights Subscriptions + version: wip + x-camara-commonalities: 0.6 + description: | + With CAMARA Connectivity Insights, application developers gain essential + visibility into network quality. This enables them to make informed + decisions that enhance the end-user experience for their applications. + + # Introduction + The Connectivity Insights API allows an application developer to ask + the network the likelihood that an application's networking + requirements can be met for a given end user session. + + This information helps a developer ensure their end users are able to + get the best experience while using the application over their current + network. + + Depending on the answer the network gives, the developer may decide to + request a network boost (via the CAMARA QoD API) , and/or apply + specific changes on the application side e.g. adjusting the + resolution of the video stream upwards or downwards. + + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Identifier for the application server**: + IPv4 and/or IPv6 address of the application server + (application backend) + + * **Notification URL and token**: + Developers may provide a callback URL on which notifications can be + received from the service provider. This is an optional parameter. + + # API functionality + + + Following diagram shows the interaction between different components + ![Sequence Diagram](https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/documentation/API_documentation/ConnectivityInsights-SequenceDiagram.png) + + ### Notification callback + + This endpoint describes the event notification received on subscription + listener side when the event occurred. As for subscription, detailed + description of the event notification is provided in the CAMARA API design + guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as + `POST /{$request.body#/sink}` will be posted by the connectivity insights + resource server to the webhook url provided by notification listener. + + ### Data Minimization + + #### phoneNumber presence: + These rules apply for subscription: + + - If 3-legged access token is used, the POST and GET{id} requests & + responses must NOT provide the ``phoneNumber``. For GET (list) only + subscription(s) for this exactly phone number is/are retrieved (implicit + filtering). + - If 2-legged access token is used, for POST and GET{id}, the presence + of``phoneNumber`` in the request & response is mandatory. For GET (list)the device identifier (``phoneNumber``) could be used as filtering criteria. + + #### sinkCredential presence: + + ``sinkCredential`` is only present in POST request and not provided in + POST or GET response. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + - When the API is invoked using a two-legged access token, the subject will + be identified from the optional `phoneNumber` identifier, which therefore + MUST be provided. + - When a three-legged access token is used however, this optional + `phoneNumber` identifier MUST NOT be provided, as the subject will be + uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged + access token to invoke the API by relying on the information that is + associated with the access token and was identified during the + authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `phoneNumber` identifier is not included in the request, then the + server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional + `phoneNumber` identifier is also included in the request, then the server + will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This + will be the case even if the same device is identified by these two + methods, as the server is unable to make this comparison. + + # Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/ConnectivityInsights/ + +servers: + - url: "{apiRoot}/connectivity-insights-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Connectivity Insights Subscriptions + description: | + Create and manage a subscription to receive periodic connectivity + insights + +paths: + /subscriptions: + post: + tags: + - Connectivity Insights Subscriptions + description: "Create a Connectivity insights subscription for a device" + summary: "Create a Connectivity insights subscription for a device" + operationId: createSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connectivity-insights-subscriptions:org.camaraproject.connectivity-insights-subscriptions.v0.network-quality:create + + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "Subscription notification callback" + description: | + Important: this endpoint is to be implemented by the API + consumer.The Connectivity Insights server will call this + endpoint whenever a connectivity event occurs that changes + the network's ability to meet the application's demands for + a given device. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json:: + schema: + $ref: "#/components/schemas/CloudEvent" + + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: | + Request accepted to be processed. It applies for async + creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connectivity Insights Subscriptions + summary: "Retrieve a list of apiName event subscription" + operationId: getSubscriptionList + description: | + Operation to list subscriptions authorized to be retrieved by the + provided access token. + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connectivity-insights-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Connectivity Insights Subscriptions + summary: "Operation to retrieve a subscription based on the provided ID" + operationId: getSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - connectivity-insights-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connectivity Insights Subscriptions + summary: "Operation to delete a subscription" + operationId: deleteSubscription + description: Delete a given subscription by ID + security: + - openId: + - connectivity-insights-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: apiName subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: | + Request accepted to be processed. It applies for async deletion + process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authorization for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: | + Subscription identifier that was obtained from the create event + subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + AdditionalKpis: + description: additional information about connectivity quality + type: object + properties: + signalStrength: + description: | + rough indication of the end user device radio signal conditions + type: string + enum: + - excellent + - good + - fair + - poor + - no signal + connectivityType: + description: | + the access technology connecting the user device to the operator + network + type: string + enum: + - 5G-SA + - 5G-NSA + - 4G + - 3G + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: | + The address to which events shall be delivered using the selected + protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + subscriptionId: + type: string + description: | + When this information is contained within an event notification, it SHALL be referred to as `subscriptionId` as per the Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + startsAt: + type: string + format: date-time + description: Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when + `subscriptionExpireTime` is indicated by API client or Telco + Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription + State engine is not mandatory for now. Note not all statuses may + be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is + triggered but subscription creation process is not finished + yet. + - `ACTIVE`: Subscription creation process is completed. + Subscription is fully operative. + - `DEACTIVE`: Subscription is temporarily inactive, but its + workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). + This status applies when subscription is ended due to + `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer + active). This status applies when subscription information is + kept (i.e. subscription workflow is no longer active but its + metainformation is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - DEACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: | + Response for a event-type subscription request managed asynchronously + (Creation or Deletion) + type: object + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: | + When this information is contained within an event notification, it SHALL be referred to as `subscriptionId` as per the Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress":"84.125.93.10", "publicPort":59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: | + Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to + clients. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + + The Operator will use this information to calculate the end to end + network performance in scenarios where its feasible. + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + ApplicationServerIpv4Address: + type: string + example: "192.168.0.1/24" + description: | + IPv4 address may be specified in form
        as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this + exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the + form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. + The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
        as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + Config: + description: | + Implementation-specific configuration parameters needed by the + subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, + `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed + event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + description: | + The subscription expiration time (in date-time format) requested by + the API consumer. Up to API project decision to keep it. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated + (>=1) requested by the API consumer - Once this number is reached, + the subscription ends. + Note on combined usage of `initialEvent` and + `subscriptionMaxEvents`: If an event is triggered following + `initialEvent` set to `true`, this event will be counted towards + `subscriptionMaxEvents`. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as + soon as the subscription is created and current situation reflects + event request. + SinkCredential: + type: object + description: | + A sink credential provides authentication or authorization information + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + CreateSubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationServerPorts: + description: | + A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + required: + - device + - applicationProfileId + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: | + The address to which events shall be delivered using the selected + protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + + NetworkQualityInsight: + type: object + description: | + the network's confidence level at being able to meet the network + demands of a given application for a given terminal device. + properties: + papplicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + packetDelayBudget: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinDownstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinUpstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + packetlossErrorRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + jitter: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + additionalKpis: + $ref: "#/components/schemas/AdditionalKpis" + + NetworkQualityThresholdsConfidence: + type: string + description: | + a plain-language indicator of how confident the network is to meet a + given network demand. + enum: + - meets the application requirements + - unable to meet the application requirements + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened, as a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + CloudEvent: + description: The Cloud-Event used for the callback. + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: | + identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: | + Version of the specification to which this event conforms (must be + 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: | + 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + $ref: "#/components/schemas/NetworkQualityInsight" + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connectivity-insights-subscriptions.v0.network-quality: + "#/components/schemas/EventNetworkQuality" + org.camaraproject.connectivityinsights.v0.eventSubscriptionEnded: + "#/components/schemas/EventSubscriptionEnded" + + EventNetworkQuality: + description: event structure for Network Quality + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/NetworkQualityInsight" + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by + the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the + requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by + the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + + EventTypeNotification: + type: string + description: | + event-type - Event triggered when an event-type event occurred + subscription-ended: Event triggered when the subscription ends + enum: + - org.camaraproject.connectivity-insights-subscriptions.v0.network-quality + - org.camaraproject.connectivity-insights-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + event-type - Event triggered when an event-type event occurred + enum: + - org.camaraproject.connectivity-insights-subscriptions.v0.network-quality + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/ConnectivityInsights/code/API_definitions/connectivity-insights/raw.md b/marked/ConnectivityInsights/code/API_definitions/connectivity-insights/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8d46b4c2c569ef8cbb25377115b0191368671bd9 --- /dev/null +++ b/marked/ConnectivityInsights/code/API_definitions/connectivity-insights/raw.md @@ -0,0 +1,695 @@ +# connectivity-insights + +```yaml +openapi: 3.0.3 +info: + title: Connectivity Insights + version: wip + x-camara-commonalities: 0.6 + description: | + With CAMARA Connectivity Insights, application developers gain essential + visibility into network quality. This enables them to make informed + decisions that enhance the end-user experience for their applications. + + # Introduction + The Connectivity Insights API allows an application developer to ask + the network the likelihood that an application's networking + requirements can be met for a given end user session. + + This information helps a developer ensure their end users are able to + get the best experience while using the application over their current + network. + + Depending on the answer the network gives, the developer may decide to + request a network boost (via the CAMARA QoD API) , and/or apply + specific changes on the application side e.g. adjusting the + resolution of the video stream upwards or downwards. + + + # API functionality + + Prerequisite: authorisation and authentication + + Usage: + 1. create an application profile using the Connectivity Insights + `application-profiles` API + 2. Request: POST `check-network-quality`, passing the + `applicationProfileId` obtained in step 1, the address/port of an + application server, and at least one device identifier. + 3. Response: The network will indicate whether it can or cannot meet + the application requirements. + 3. Optional: use the `connectivity-insights-subscriptions` API to receive + notifications of network quality. + + Following diagram shows the interaction between different components + ![Sequence Diagram](https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/documentation/API_documentation/ConnectivityInsights-SequenceDiagram.png) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/ConnectivityInsights + +servers: + - url: "{apiRoot}/connectivity-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Network Quality + description: | + Read the network's level of confidence that it can meet the quality + thresholds for a given application profile and end user device. + +paths: + /check-network-quality: + post: + security: + - openId: + - connectivity-insights:check + tags: + - Network Quality + summary: Check the network quality. + description: | + Check the network quality. The response shows the network's current + level of confidence that it can meet an application profile's quality + thresholds for a given end user device. + operationId: checkNetworkQuality + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: | + An `ApplicationProfileId` and one or more device identifiers. + Together these allow the network to calculate whether the thresholds + defined in the application profile can be met for the particular + connected device. + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkQualityInsightRequest" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/NetworkQualityInsightResponse" + - $ref: "#/components/schemas/DeviceResponseBody" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkQualityInsightRequest: + description: | + request body to query the network quality for a given device and + application profile + type: object + properties: + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationServerPorts: + description: | + A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + monitoringTimeStamp: + type: string + format: date-time + description: | + this is an optional input parameter. A future data and time can be + provided for predictive data. If no value is provided then the + current date and time is used and network data for the monitoring + data aggregation is used to check network performance against the + application profile defined. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + + NetworkQualityInsightResponse: + type: object + description: the network's confidence level at being able to meet the + network demands of a given application for a given terminal device. + properties: + packetDelayBudget: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinDownstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinUpstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + packetlossErrorRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + jitter: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + additionalKPIs: + $ref: "#/components/schemas/AdditionalKpis" + + AdditionalKpis: + description: additional information about connectivity quality + type: object + properties: + signalStrength: + description: | + rough indication of the end user device radio signal conditions + type: string + enum: + - excellent + - good + - fair + - poor + - no signal + connectivityType: + description: | + the access technology connecting the user device to the operator + network + type: string + enum: + - 5G-SA + - 5G-NSA + - 4G + - 3G + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The + API invoker can provide multiple identifiers to be compatible across + different MNOs. In this case the identifiers MUST belong to the same + device. + NOTE2: for the Commonalities release v0.4, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + optionally prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + DeviceResponseBody: + description: | + The optional device identifier to include in the response + properties: + device: + description: | + The device identifier that was used to fulfil the request. + If this property is not present then the device + identifier sent in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to + clients. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + + The Operator will use this information to calculate the end to end + network performance in scenarios where its feasible. + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + ApplicationServerIpv4Address: + type: string + example: "192.168.0.1/24" + description: | + IPv4 address may be specified in form
        as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this + exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the + form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. + The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
        as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + NetworkQualityThresholdsConfidence: + type: string + description: | + a plain-language indicator of how confident the network is to meet a + given network demand. + enum: + - meets the application requirements + - unable to meet the application requirements + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not available for the provided device + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The Service is not available for the provided device. + GENERIC_422_MISSING_IDENTIFIER: + description: + An identifier is not included in the request and the device or phone + number identificationinformation cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist/raw.md b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..43949a0837c02225ddd8fbb5ac41f38b47e33c1b --- /dev/null +++ b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for connectivity-insights v0.6.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/connectivity-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/ConnectivityInsights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/connectivity-insights.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/K4HWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story/raw.md b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3d00029979c3d4a1bcb4ada80abe9838b1ea49d7 --- /dev/null +++ b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story/raw.md @@ -0,0 +1,10 @@ +# Connectivity Insights API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to be able to understand my application's network performance demands and determine the likelihood that the network will be able to meet those demands. I can represent my application's network performance demands as a set of metrics (latency, jitter, loss, throughput) and register these with the network using Application Profiles. At runtime, I can query the network to determine if a given device is likely to receive that level of network performance across each metric. In addition, I would like to receive notifications when the network is unable to meet the network performance thresholds for specific device. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
        **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
        **Scope:**
        • Perform network quality check againt the application profile for specific user sessions
        • Create subscriptions to recieve notifications if the network is not able to meet the application's requirements
        | +| ***Pre-conditions*** |The preconditions are listed below:
        1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platfrom.
        2. The API Consumer:BusinessManager has successfully subscribed to the Connectivity Insights product from the product catalog.
        3. The API Consumer:Administrator has onboarded the developer:User to the platform.
        4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
        5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:**
          1. The API consumer application server makes a POST request to the check-network-quality endpoint to query if the network can meet the application profile requirements for a specific device.
          2. Optionally, the API consumer application server creates a subscription to receive notifications about network quality changes.

          **Ends when:**
          1. The API endpoint is able to report whether the network can meet the application requirements or not for a given device. or
          2. The monitoring session resource deletion was triggered automatically because the requested duration has expired or the maximum number of events was reached. | +| ***Post-conditions*** | 1. none for synchronous network quality check API.
          2. If subscriptions are created, notifications are sent when network quality changes affect the ability to meet application requirements until the subscription is deleted or has expired.| +| ***Exceptions*** | Several exceptions might occur
          - Unauthorized: Not valid credentials (e.g. use of already expired access token).
          - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
          - Conflict: Internal configuration didn’t allow for operations.
          - Not Found: Requested Application Profile ID or Subscription ID doesn't exist.
          - Session-not-created: Due to other internal errors| diff --git a/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist/raw.md b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..046c7056dc7c3127588651be81f80153c0300d73 --- /dev/null +++ b/marked/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for connectivity-insights-subscriptions v0.6.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/connectivity-insights-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/ConnectivityInsights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/connectivity-insights-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/GIBSBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06/raw.md b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..af19758399d4735bd7de78c738c56106626e30d8 --- /dev/null +++ b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06/raw.md @@ -0,0 +1,31 @@ +# Minutes of Connectivity Insights, 6th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +- #3 initial upload of Connectivity Insights YAML +- #4 call schedule + +## Issues +None + +## Discussions +- Administriva (call schedule, need for sub-project to be added to CAMARA wiki) +- Need for API to align with API Design guidelines (initial commit is based on 5GFF) +- Uncertainty regarding consent: who decides whether it is required for this API, the sub-project, The Identity and Consent Project, the TSC, the Stterco? + + +## Actions +- Mahesh to mail the mailing list with call details and update time on GitHub +- Mahesh to align the Connectivity Insights API spec with commonalities guidelines. +- Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. +- Kevin to add Connectivity Insights to CAMARA Wiki + +# AOB + +## Date of next meeting +13th December 2023, 1500 UTC +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13/raw.md b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..53a1f50313d88abbf83bd24990342f1e2b53a354 --- /dev/null +++ b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13/raw.md @@ -0,0 +1,66 @@ +# Minutes of Connectivity Insights, 13th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Santhi Dharmapalan/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Open: +- [#7 Update CAMARA Connectivity Insights API.yaml](https://github.com/camaraproject/ConnectivityInsights/pull/7) fixes [#6](https://github.com/camaraproject/ConnectivityInsights/issues/6) + +Merged since last call: +- #3 initial upload of Connectivity Insights YAML +- #4 call schedule +- #5 update maintainers + +## Issues +Open: +- [#6](https://github.com/camaraproject/ConnectivityInsights/issues/6) API basepath should be human-readable + + This is awaiting confirmation from Herbert that his requested changes are reflected + +- [#9](https://github.com/camaraproject/ConnectivityInsights/issues/9) Performance metric definitions do not match those of the QoD API + + Agreement to adopt the QoD schema. + +## Discussions +- Completed actions were confirmed: + + DONE Mahesh to mail the mailing list with call details and update time on GitHub + + DONE Kevin to add Connectivity Insights to CAMARA Wiki + +- Discussion on whether we need for port identification at both Device and Application port side + + Agreed we would need this for Connectivity Insights between a given device and application server. + The device IPv4 address and public port can be sent by the API consumer, but we will not need to user the private port (pre-NAT) in the API. + The schema deifintions will be reused from QoD. + +- Issues: see discussion and resolution in 'Issues' section above. + +## Actions +Open: +1. Mahesh to align the Connectivity Insights API spec with commonalities guidelines. + - Mahesh will add documentation (similar to QoD) and is going through the API Design Guidelines to align + - Response codes will be adopted from QoD + - we will add cloud notifications in a later release (for now focus is the main API Design guidelines) + +2. Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. + +## AOB + +None + +## Date of next call + +1500 UTC, 1 hour, [Webex link](https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a) + +# AOB + +None + +## Date of next meeting + +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20/raw.md b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7d95d1f9fd29d8665655d7986838592b3a11b222 --- /dev/null +++ b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20/raw.md @@ -0,0 +1,54 @@ +# Minutes of Connectivity Insights, 20th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Santhi Dharmapalan/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Merged since last call: +- #7 , #8, #10, #11, 15 + +Open: +- #16 updated documentation to include User Story and API readiness checklist +- - Mahesh has seen the comments and is working on them +- #19 Create Megalinter +- - merged during call + +## Issues +Open: +- #17 Event subscription and notifications should be aligned with API Design Guidelines +- - assigned to Kevin +- #18 Alignment with API design guidelines: add linter +- - fixed by #19 (now merged) + +## Discussions +- Completed actions were confirmed: + + IN PROGRESS Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. + + Guidance from commonalities is to include a security component but with an empty scope until this is clarified. + +- Issues: see discussion and resolution in 'Issues' section above. + +- Question: can megalinter be run outside Github (as a precheck)? + +- Labels added to issues and PRs: 0-2-0-wip and 0-3-0-wip. These indicate the target version for the issue/PR (i.e. 'this issue is intended to be fixed in 0-3-0-wip', 'this PR is to create the 0-3-0-wip version' +) +## Actions +Open: +1. Mahesh to align the Connectivity Insights API spec with commonalities guidelines. + - Mahesh will add documentation (similar to QoD) and is going through the API Design Guidelines to align + - Response codes will be adopted from QoD + - we will add cloud notifications in a later release (for now focus is the main API Design guidelines) +2. Kevin to check if megalinter can be run outside Github as a pre-check + +## AOB + +None + +## Date of next meeting +January 3rd 2024 +1500 UTC, 1 hour, [Webex link](https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a) +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19/raw.md b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f5a5fe97d70e0a59648a7989e260aed1a7ef71ef --- /dev/null +++ b/marked/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19/raw.md @@ -0,0 +1,46 @@ +# Minutes of Connectivity Insights, 19th January 2024 + +## Attendees +* Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +* Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Merged since last call: +* #22 YAML update following the running of Spectral/Megalinter to fix misalignment with CAMARA guidelines + +Open: +* #16 updated documentation to include User Story and API readiness checklist: +-> Mahesh has seen the comments and is working on them + +## Issues +Open: +* none + +Closed since last call: +* #6, #9, #12, #13, #14, #17, #18, #21 + +## Discussions +* 0-3-0 is almost ready to release, but requires CAMARA consent guidelines to be added (see Action (A3) below) +* We also need to add the Test Definitions. (see Action (A4) below) +* The repo now has 'Discussions' enabled. Kevin has added the Spectral output for the latest YAML commit. +* Kevin will add a discussion on the name of the paths used for the API, as they seem telco-centric and misleading. + +## Actions +Closed: + +~~(A1)Mahesh to align the Connectivity Insights API spec with commonalities guidelines.~~ + +~~(A2)Kevin to check if megalinter can be run outside Github as a pre-check~~ + +New: +* (A3)Kevin will add the consent components and documentation as per [Identity and Consent common guidelines](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md#camara-api-specification---authorization-and-authentication-common-guidelines) +* (A4) Mahesh will investigate developing the Gherkin `.feature` file for test defintions. + +## AOB + +Meetings to now be bi-weekly following as we now have a stable draft API + +## Date of next meeting +January 31st 2024 +1500 UTC, 1 hour, [Webex link]([https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a](https://eur03.safelinks.protection.outlook.com/?url=https%3A%2F%2Fverizon.webex.com%2Fverizon%2Fj.php%3FMTID%3Dmfd368abae20d28d9ec122b91846fd618&data=05%7C02%7Ckevin.smith%40vodafone.com%7Ce80185de42a74c7b9a0708dc17660ed7%7C68283f3b84874c86adb3a5228f18b893%7C0%7C0%7C638410975421905374%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C41000%7C%7C%7C&sdata=O4mlK0Rvdj2CQY0u36W2A8o9Ld70m9lI2DOBFiReBKA%3D&reserved=0)https://eur03.safelinks.protection.outlook.com/?url=https%3A%2F%2Fverizon.webex.com%2Fverizon%2Fj.php%3FMTID%3Dmfd368abae20d28d9ec122b91846fd618&data=05%7C02%7Ckevin.smith%40vodafone.com%7Ce80185de42a74c7b9a0708dc17660ed7%7C68283f3b84874c86adb3a5228f18b893%7C0%7C0%7C638410975421905374%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C41000%7C%7C%7C&sdata=O4mlK0Rvdj2CQY0u36W2A8o9Ld70m9lI2DOBFiReBKA%3D&reserved=0) + diff --git a/marked/ConnectivityInsights/documentation/MeetingMinutes/README/raw.md b/marked/ConnectivityInsights/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConnectivityInsights/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConnectivityInsights/documentation/SupportingDocuments/README/raw.md b/marked/ConnectivityInsights/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConnectivityInsights/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConsentInfo/README/raw.md b/marked/ConsentInfo/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f177e7cb8dabc973450dc484e92a8b1b0fcd78ab --- /dev/null +++ b/marked/ConsentInfo/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# ConsentInfo + +Sandbox API Repository to describe, develop, document, and test the ConsentInfo API(s) within the Working Group [IdentityAndConsentManagement](https://lf-camaraproject.atlassian.net/wiki/x/ZzDe) + +* API Repository [Wiki page](https://lf-camaraproject.atlassian.net/wiki/x/NICeBQ) + + +## Scope + +* Service APIs for “ConsentInfo" (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * **Check the validity of data processing**: The API returns `statusValidForProcessing`, a boolean flag that indicates whether the requested data processing is currently permitted (`true`) or not (`false`). + * **Understand why processing is not allowed**: If data processing is not permitted, the response includes a `statusReason` field to explain why. + * **Retrieve a Capture URL (if requested)**: If the status is not valid because user action is required, and the API Consumer sets `requestCaptureUrl` to `true`, the API will return a `captureUrl` field that can be presented to the User. This URL directs them to the API Provider's secure Consent capture channel, where they can provide or renew their Consent. + + Importantly, this API does NOT delegate Consent capture to the API Consumer but rather empowers the API Consumer to present the API Provider's Consent capture URL at the most opportune time and place. The actual Consent capture occurs within the API Provider's secure environment, ensuring the User's authentication with the API Provider. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* The latest public release is [r2.3](https://github.com/camaraproject/ConsentInfo/releases/tag/r2.3), with the following API versions: + * **consent-info 0.2.0** + [[YAML]](https://github.com/camaraproject/ConsentInfo/blob/r2.3/code/API_definitions/consent-info.yaml) [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConsentInfo/r2.3/code/API_definitions/consent-info.yaml&nocors) [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConsentInfo/r2.3/code/API_definitions/consent-info.yaml) + +* The latest public release is always available here: https://github.com/camaraproject/ConsentInfo/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConsentInfo/releases +* For changes see [CHANGELOG](https://github.com/camaraproject/ConsentInfo/tree/main/CHANGELOG) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings of the working group are held virtually + * Schedule: Every 2 weeks on Wednesdays at 14:00 UTC (IdentityAndConsentManagement Working Group meeting) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94629188836?password=278b4c8a-f370-43bf-bac1-b30a39f169f3) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/lE7e) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ConsentInfo/code/API_definitions/consent-info/raw.md b/marked/ConsentInfo/code/API_definitions/consent-info/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1150597a576236845da4d578a0b3b8f007d5549e --- /dev/null +++ b/marked/ConsentInfo/code/API_definitions/consent-info/raw.md @@ -0,0 +1,640 @@ +# consent-info + +```yaml +openapi: 3.0.3 +info: + title: Consent Info + description: | + The Consent Info API allows API Consumers to easily validate whether they have the necessary permissions to process User's personal data for a specific Purpose before using other CAMARA APIs. It provides a simple `true`/`false` response and, when applicable, a URL to direct the User to manage their Consent. + + # Introduction + + This API facilitates compliance with privacy regulations and promotes transparency with Users by providing a standardized way to check whether, for example, the User has given their Consent or opted out of data processing. Key inputs include the specific scope(s) of access being requested (i.e. the CAMARA API(s) operations to which the data processing refers), the Purpose for data processing, and a User identifier (either explicitly provided or derived from a three-legged access token). The API responds with the validity status of the data processing, and, when applicable, can provide a capture URL for the API Consumer to manage it. + + # Relevant terms and definitions + + * **Consent**: An explicit opt-in action that the User takes to allow processing of personal data. Consent grants the API Consumer access to a set of scopes related to the User for a specific Purpose. + * **Purpose**: The reason for which personal data will be processed by an API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + * **Scope**: A string representing the specific access rights or actions an API Consumer requests from the User for their data (e.g., "location-verification:verify"). A request can contain multiple scopes. + + # API Functionality + + This API enables the API Consumer to determine whether their data processing is permitted for a given User, scope(s) and Purpose. + + Specifically, the API: + + * **Provides the data processing validity status**: The API returns `statusValidForProcessing`, a boolean flag that indicates whether the requested data processing is currently permitted (`true`) or not (`false`). + * **Provides an explanation if invalid**: If data processing is not permitted, the response includes a `statusReason` field to explain why. + * **Offers a Capture URL (if requested)**: If the status is not valid because user action is required, and the API Consumer sets `requestCaptureUrl` to `true`, the API will return a `captureUrl` field that can be presented to the User. This URL directs them to the API Provider's secure Consent capture channel, where they can provide or renew their Consent. + * **Supports Callback URL**: The API Consumer can optionally provide a `callbackUrl` when requesting a Consent capture URL. This allows the API Provider to redirect the User back to the API Consumer's specified URL once the Consent capture process is completed, along with the outcome of the process. + + Importantly, this API does NOT delegate Consent capture to the API Consumer but rather empowers the API Consumer to present the API Provider's Consent capture URL at the most opportune time and place. The actual Consent capture occurs within the API Provider's secure environment, ensuring the User's authentication with the API Provider. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared Purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConsentInfo +servers: + - url: "{apiRoot}/consent-info/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Retrieve Status + description: Create a request to retrieve the validity status of the data processing +paths: + /retrieve: + post: + summary: Create a request to retrieve the validity status of the data processing + description: | + Create a request to retrieve the validity status of the API Consumer data processing for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + operationId: retrieveStatus + security: + - openId: + - consent-info:retrieve + tags: + - Retrieve Status + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + description: Retrieve status request + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveStatusRequestBody" + examples: + ONE_SCOPE_ONE_API: + summary: One scope + description: | + Request with one scope corresponding to one API + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + MULTIPLE_SCOPES_ONE_API: + summary: Multiple scopes for one API + description: | + Request with multiple scopes corresponding to one API + value: + phoneNumber: "+123456789" + scopes: + - "quality-on-demand:sessions:create" + - "quality-on-demand:sessions:read" + - "quality-on-demand:sessions:update" + - "quality-on-demand:sessions:delete" + - "quality-on-demand:sessions:retrieve-by-device" + purpose: "dpv:RequestedServiceProvision" + requestCaptureUrl: true + MULTIPLE_SCOPES_MULTIPLE_APIS: + summary: Multiple scopes for multiple APIs + description: | + Request with multiple scopes corresponding to multiple APIs + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + ONE_SCOPE_CALLBACK_URL: + summary: One scope with callback URL + description: | + Request with one scope corresponding to one API including a callback URL + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + callbackUrl: "https://consumer.example.com/consent/callback" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveStatusResponseBody" + examples: + READY_FOR_PROCESSING: + summary: Ready for processing + description: | + Data processing is allowed for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: true + CONSENT_REQUIRED: + summary: Consent is required + description: | + Consent is required for the requested scope(s) and Purpose + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: REQUESTED + CONSENT_REQUIRED_CAPTURE_URL: + summary: Consent is required and capture URL is provided + description: | + Consent is required for the requested scope(s) and Purpose but it is expired. The API Provider provides a Consent capture URL. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: EXPIRED + expirationDate: "2023-07-03T14:27:08.312+02:00" + captureUrl: "https://example.org/consent-capture-url" + CONSENT_DENIED: + summary: Consent is denied + description: | + Consent is denied for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: DENIED + DATA_PROCESSING_OPT_OUT: + summary: Data processing opt-out + description: | + The User has opted out of the data processing for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: OBJECTED + MULTIPLE_SCOPES_ONE_API: + summary: Multiple scopes for one API + description: | + Request with multiple scopes corresponding to one API. + value: + statusInfo: + - scopes: + - "quality-on-demand:sessions:create" + - "quality-on-demand:sessions:read" + - "quality-on-demand:sessions:update" + - "quality-on-demand:sessions:delete" + - "quality-on-demand:sessions:retrieve-by-device" + purpose: "dpv:RequestedServiceProvision" + statusValidForProcessing: true + MULTIPLE_SCOPES_MULTIPLE_APIS: + summary: Multiple scopes for multiple APIs + description: | + Request with multiple scopes corresponding to multiple APIs. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: PENDING + - scopes: + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: PENDING + captureUrl: "https://example.org/consent-capture-url" + MULTIPLES_SCOPES_ONE_API_DIFFERENT_STATUS: + summary: Multiple scopes for one API with different status + description: | + Request with multiple scopes corresponding to one API. Different status for each scope. + value: + statusInfo: + - scopes: + - "sim-swap:check" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: true + - scopes: + - "sim-swap:retrieve-date" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: OBJECTED + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/retrieveStatus403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + RetrieveStatusRequestBody: + type: object + description: | + The request body for the retrieve status request. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data, a flag indicating whether the API Consumer requests a Consent capture URL and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - requestCaptureUrl + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + requestCaptureUrl: + type: boolean + description: | + A boolean flag indicating whether the API Consumer requests API Provider to return a Consent capture URL. + * `true` - If set to `true` the API will include a `captureUrl` in the response body if applicable. + * `false` - The API will omit the Consent capture URL from the response. + example: true + callbackUrl: + type: string + format: uri + description: | + Optional URL to which the User shall be redirected by the API Provider once the Consent Capture process has reached a final state (e.g., The User has given their consent). This parameter is only applicable when the API Consumer requests a Consent capture URL by setting `requestCaptureUrl` to `true`. + + The `callbackUrl` parameter enables API Consumers to seamlessly regain control of the user experience once the Consent Capture journey is completed. + + **Functional behaviour** + + When the `callbackUrl` is provided in the request, the API Provider MUST redirect the User to this URL upon completion of the Consent Capture journey. The redirection MUST include a query parameter named `capture_result` that indicates the outcome of the Consent Capture process. The possible values for `capture_result` are: + + - `granted`: The User has successfully provided Consent for the specified scope(s) and Purpose. + - `partial_grant`: The User has provided Consent for only a subset of the originally requested scopes and Purpose. When a `partial_grant` is returned, the API Provider MUST ensure that subsequent API requests reflect the precise subset of scopes actually authorized. + - `denied`: The User has explicitly denied the Consent for the specified scope(s) and Purpose. + - `error`: The Consent Capture flow terminated abnormally due to an internal error, network issue, or unexpected failure. + - `timeout`: The User did not complete the Consent Capture flow within the defined timeout period. + + The API Consumer MAY include a `state` query parameter when initiating the Consent Capture journey (i.e., when opening the Consent Capture URL) to correlate the process with an existing session or transaction context. If the state parameter is provided, the API Provider MUST preserve its value and append it unchanged to the callback URL when redirecting the User at the end of the journey. + + e.g. `https://consumer.example.com/consent/callback?capture_result=granted&state=xyz123` + + **Security considerations** + + - The `callbackUrl` MUST use the `https` scheme to ensure transport security. + Exceptions MAY be allowed for loopback addresses (`http://127.0.0.1`, `http://[::1]`, or `http://localhost`) + or for custom application schemes (e.g., `myapp://consent/callback`) when used as secure deep links + for native applications. + - The `callbackUrl` SHOULD be validated by the API Provider to prevent open redirect or injection attacks. + Validation SHOULD ensure that the domain or scheme is either pre-registered or demonstrably under the + control of the API Consumer. + - The API Provider MUST NOT include any personal data, access tokens, or identifiers in the callback URL. + The `capture_result` parameter MUST be appended, as MUST the `state` parameter if it has been received previously. + - The API Consumer SHOULD validate the origin of incoming callbacks and confirm that the received parameters + correspond to an expected session or flow (e.g., by verifying the `state` value to prevent CSRF attacks). + example: "https://consumer.example.com/consent/callback" + Scopes: + type: array + minItems: 1 + items: + type: string + description: | + List of requested scopes. The scope is a string that represents the access rights that the API Consumer is requesting from the User. + example: + - "location-verification:verify" + Purpose: + type: string + pattern: '^dpv:[a-zA-Z0-9]+$' + description: | + The reason for which personal data will be processed by the API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + example: "dpv:FraudPreventionAndDetection" + RetrieveStatusResponseBody: + type: object + required: + - statusInfo + properties: + statusInfo: + $ref: "#/components/schemas/statusInfo" + captureUrl: + type: string + format: url + description: | + URL where the User can provide the necessary Consent. This field is only present in the API response if the API Consumer requests it and if the following conditions are met: + + - `statusInfo[*].statusValidForProcessing` is `false`, and + - `statusInfo[*].statusReason` is `PENDING`, `REQUESTED` or `EXPIRED`. + + Please note that this field is only applicable when the User Consent is required to enable valid data processing. A unique URL is provided to authorise all items in the statusInfo list that require user action. + example: "https://example.org/consent-capture-url" + statusInfo: + type: array + description: | + Provides information about the validity status of the requested data processing for the specified scope(s) and Purpose. It contains details of whether the processing of the data is currently valid and, if not, the reason why. The expiration date of the validity may be also provided if applicable. + + More than one array item may be required for the requested scope(s) and Purpose, e.g. when the requested scopes relate to multiple APIs. + items: + $ref: "#/components/schemas/statusInfoObject" + minItems: 1 + statusInfoObject: + type: object + required: + - scopes + - purpose + - statusValidForProcessing + properties: + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + statusValidForProcessing: + type: boolean + description: | + Boolean flag that shows the validity status of the requested data processing for the specified scope(s) and Purpose. + * `true` - indicates that the current status is valid and permits the requested data processing. + * `false` - indicates that the requested data processing is not permitted. The reason for this is provided in the `statusReason` field. + statusReason: + type: string + enum: + - PENDING + - REQUESTED + - DENIED + - EXPIRED + - OBJECTED + description: | + This field must be present if `statusValidForProcessing` is `false`. It indicates the reason why the requested data processing is not permitted for the specified scope(s) and Purpose. It provides API Consumers with additional context on the current validity status, helping them to understand its applicability and the next steps they may need to take. + + It is particularly useful for determining whether the API Consumer should prompt the User to take action, such as providing Consent or renewing an existing Consent. + + Possible values are: + + - `PENDING`: The requested data processing has not yet been established or fully validated under the applicable privacy regulations. + For example, the User has not yet provided Consent when it is required. + - `REQUESTED`: The permission for the requested data processing has been submitted but has not yet been granted or confirmed. + This is common when the API Consumer has initiated a request for Consent capture, but the User has not yet completed the process. For example, this occurs when a notice prompting the User to provide Consent has been displayed, but they have not yet made a decision. + - `DENIED`: The User has explicitly refused their permission for the requested data processing. + For example, when the User refuses to grant Consent for the data processing, or when they previously granted Consent but later withdrew it. + - `OBJECTED`: The user has opted out of the requested data processing, despite a previous explicit opt-in not being required. + This is common when the User has exercised their right to object to data processing under the applicable privacy regulations. + - `EXPIRED`: When applicable, the validity of the data processing has ceased due to the passage of time or a pre-defined condition. + This is common for time-limited Consents. + expirationDate: + type: string + format: date-time + description: | + The date and time at which the validity of the data processing is set to expire or has expired. + It applies mainly to time-limited Consents, or other cases where a specific duration of validity is defined for the data processing. This field is only applicable: + + - if `statusValidForProcessing` is `true` (indicating a future expiration), or + - if `statusValidForProcessing` is `false` and `statusReason` is `EXPIRED` (indicating the past expiration date). + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2023-07-03T14:27:08.312+02:00" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + retrieveStatus403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CONSENT_INFO.NOT_ALLOWED_SCOPES_PURPOSE + - CONSENT_INFO.CAPTURE_FREQUENCY_EXCEEDED + - CONSENT_INFO.INVALID_CALLBACK_URL + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + NOT_ALLOWED_SCOPES_PURPOSE: + description: The requested scope(s) and Purpose combination is not allowed for the API Consumer, e.g. the API Consumer has not onboarded the appropriate API(s) with the API Provider for the declared Purpose. + value: + status: 403 + code: CONSENT_INFO.NOT_ALLOWED_SCOPES_PURPOSE + message: The requested scope(s) and Purpose combination is not allowed for this API Consumer. + CAPTURE_FREQUENCY_EXCEEDED: + description: The frequency of consent capture requests has been exceeded. + value: + status: 403 + code: CONSENT_INFO.CAPTURE_FREQUENCY_EXCEEDED + message: The frequency of consent capture requests has been exceeded. Please try again later. + INVALID_CALLBACK_URL: + description: The provided callback URL is invalid. + value: + status: 403 + code: CONSENT_INFO.INVALID_CALLBACK_URL + message: The provided callback URL is invalid. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration +``` diff --git a/marked/ConsentInfo/documentation/SupportingDocuments/README/raw.md b/marked/ConsentInfo/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConsentInfo/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConsentManagement/README/raw.md b/marked/ConsentManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5c71edd40871234ab8a6f4416e487dff1754456f --- /dev/null +++ b/marked/ConsentManagement/README/raw.md @@ -0,0 +1,46 @@ + + + + + + + + + +# ConsentManagement + +Sandbox API Repository to describe, develop, document, and test the ConsentManagement Service API(s) within the Working Group [Identity And Consent Management](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14561383/Identity+Consent+Management). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/WgDDH) + +## Scope + +* Service API(s) “ConsentManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * **Create Consent**: Allows API Consumers to create a new Consent for a User, specifying the requested scope(s) and Purpose. The API Consumer must provide the necessary information to capture the User's Consent. + * **Update Consent**: Enables API Consumers to update an existing Consent and change its status. + * **Retrieve Consent Information**: Allows API Consumers to retrieve information about existing Consents for a User based on specified scope(s) and Purpose. This operation can also return the Consent texts presented to the User during the Consent Capture process if requested. + + It is important to note that the API Provider remains fully responsible for Consent storage, auditing and transparency. Access to this functionality is restricted to trusted API Consumers in accordance with the API Provider's policy. This API only applies to scenarios involving the legal basis of Consent. Scenarios involving a different legal basis for data processing are excluded and would be handled by the API Provider through non-delegated mechanisms. +* Describe, develop, document, and test the API(s) +* Started: December 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: Every 2 weeks on Wednesdays at 14:00 UTC (IdentityAndConsentManagement Working Group meeting) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94629188836?password=278b4c8a-f370-43bf-bac1-b30a39f169f3) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/lE7e) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of the Working Group can be sent using . diff --git a/marked/ConsentManagement/code/API_definitions/consent-management/raw.md b/marked/ConsentManagement/code/API_definitions/consent-management/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d8764f2a157fd51232869e1521c81647ecb11b46 --- /dev/null +++ b/marked/ConsentManagement/code/API_definitions/consent-management/raw.md @@ -0,0 +1,960 @@ +# consent-management + +```yaml +openapi: 3.0.3 +info: + title: Consent Management + description: | + This API enables API Consumers to manage User Consents for accessing personal data via CAMARA APIs. It allows creating, updating, and retrieving Consent information based on specific scope(s) and Purpose in the API Provider's Consent Management system. + + # Introduction + + In the context of CAMARA, Consent Management refers to the processes and mechanisms that allow API Consumers to obtain, manage, and verify User Consents for accessing and processing personal data through CAMARA APIs. This API specification defines the operations and data structures necessary for API Consumers to interact with Consent Management services provided by API Providers. + + This optional, controlled delegation model enables trusted API Consumers to capture the User Consent directly within their own applications using Consent texts and parameters provided by API Providers. This model aims to streamline the User Consent capture process, enhance User experience, and ensure compliance with data protection regulations by leveraging API Provider-verified Consent texts. + + # Relevant terms and definitions + + * **Consent**: An explicit opt-in action that the User takes to allow processing of personal data. Consent grants the API Consumer access to a set of scopes related to the User for a specific Purpose. + * **Purpose**: The reason for which personal data will be processed by an API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + * **Scope**: A string representing the specific access rights or actions an API Consumer requests from the User for their data (e.g., "location-verification:verify"). A request can contain multiple scopes. + + # API Functionality + + This Consent Management API provides the following key functionalities: + + - **Create Consent**: Allows API Consumers to create a new Consent for a User, specifying the requested scope(s) and Purpose. The API Consumer must provide the necessary information to capture the User's Consent. + - **Update Consent**: Enables API Consumers to update an existing Consent and change its status. + - **Retrieve Consent Information**: Allows API Consumers to retrieve information about existing Consents for a User based on specified scope(s) and Purpose. This operation can also return the Consent texts presented to the User during the Consent Capture process if requested. + + It is important to note that the API Provider remains fully responsible for Consent storage, auditing and transparency. Access to this functionality is restricted to trusted API Consumers in accordance with the API Provider's policy. This API only applies to scenarios involving the legal basis of Consent. Scenarios involving a different legal basis for data processing are excluded and would be handled by the API Provider through non-delegated mechanisms. + + ## Consent status lifecycle + + A User Consent follows a defined status lifecycle. The possible statuses and their allowed transitions are described below and illustrated in the diagram: + + - **PENDING**: Initial status indicating that the User Consent has not yet been requested from the User. No Consent record (`consentId`) exists at this stage. + - **REQUESTED**: The User Consent has been requested from the User, but the User has not yet responded. A Consent record exists with a `consentId`. + - **GRANTED**: The User has approved the Consent, allowing the requested data processing. This status is set when creating or updating a Consent with status `GRANTED`. + - **DENIED**: The User has rejected the Consent. This status is set when creating or updating a Consent with status `DENIED`. + - **EXPIRED**: The User Consent has expired because its TTL (time-to-live) has been reached. Both `GRANTED` and `DENIED` Consents can expire. The API Provider determines the expiration date based on its internal policies. + + The allowed transitions are: + + - `PENDING/REQUESTED` → `GRANTED`: The User approves the Consent. + - `PENDING/REQUESTED` → `DENIED`: The User rejects the Consent. + - `GRANTED` → `DENIED`: The User revokes a previously granted Consent. + - `DENIED` → `GRANTED`: The User reconsents after previously denying. + - `GRANTED` → `EXPIRED`: The Consent TTL is reached and the Consent expires. + - `DENIED` → `EXPIRED`: The Consent TTL is reached and the Consent expires. + - `EXPIRED` → `GRANTED`: The User renews and approves an expired Consent. It requires the API Consumer to recapture the User Consent and update the Consent status to `GRANTED` via the `updateConsent` operation. + - `EXPIRED` → `DENIED`: The User renews and rejects an expired Consent. It requires the API Consumer to recapture the User Consent and update the Consent status to `DENIED` via the `updateConsent` operation. + + Note that API Consumers can only set a Consent status to `GRANTED` or `DENIED` via the `createConsent` and `updateConsent` operations. The `PENDING`, `REQUESTED`, and `EXPIRED` statuses are managed by the API Provider. + + The following diagram illustrates the allowed status transitions: + + ``` + +-----------------+ + |PENDING/REQUESTED| + +--+------------+-+ + | | + User Rejects User Approves + +--------+ +-------+ + | | + +-----v--------+ +-------v------+ + | <-Revocation-+ | + | DENIED +-Re-consent-> GRANTED | + | +-+ +-+ | + +---^----------+ | | +--------^-----+ + | | | | + | TTL Reached | | + | | | | + | | TTL Reached | + | | | | + Renewed | | Renewed + & Rejected +--v--------v--+ & Approved + | | | | + +---------+ EXPIRED +-------+ + | | + +--------------+ + ``` + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared Purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConsentInfo +servers: + - url: "{apiRoot}/consent-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Consent Management + description: Operations to manage User's Consent +paths: + /consents: + post: + summary: Create User Consent + description: | + This operation allows the API Consumer to create a Consent for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The API Provider will set the creation date of the User Consent to the current date and time when the `createConsent` operation is invoked successfully by the API Consumer. + + The expiration date of the User Consent created by the API Consumer will be determined by the API Provider's internal policies. The API Consumer cannot set or modify the expiration date of the User Consents captured in a delegated manner. + operationId: createConsent + security: + - openId: + - consent-management:create + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + description: createConsent operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/CreateConsentRequestBody" + examples: + CREATE_CONSENT_REQUEST_GRANTED: + summary: Create Consent request with status GRANTED + value: + phoneNumber: "+123456789" + scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "GRANTED" + consentTextId: "pp-sha256-a1b2c3d4..." + CREATE_CONSENT_REQUEST_DENIED: + summary: Create Consent request with status DENIED + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "DENIED" + consentTextId: "pp-sha256-a1b2c3d4..." + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateConsentResponseBody" + examples: + CREATE_CONSENT_RESPONSE: + summary: Create Consent response + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + CREATE_CONSENT_RESPONSE_EXPIRATION_DATE: + summary: Create Consent response with expiration date + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + "400": + $ref: "#/components/responses/Consent400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Consent403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + /consents/{consentId}: + patch: + summary: Update User Consent + description: | + This operation allows the API Consumer to update the status of an existing Consent for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The expiration date of the User Consent updated by the API Consumer will be determined by the API Provider's internal policies. The API Consumer cannot set or modify the expiration date of the User Consents captured in a delegated manner. + operationId: updateConsent + security: + - openId: + - consent-management:update + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: consentId + in: path + required: true + description: The unique identifier of the User Consent + schema: + type: string + example: "consent-123456" + requestBody: + required: true + description: updateConsent operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/UpdateConsentRequestBody" + examples: + UPDATE_CONSENT_REQUEST_DENIED: + summary: Update Consent status to DENIED + value: + consentStatus: "DENIED" + UPDATE_CONSENT_REQUEST_GRANTED: + summary: Update Consent status to GRANTED + value: + consentStatus: "GRANTED" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/UpdateConsentResponseBody" + examples: + UPDATE_CONSENT_RESPONSE: + summary: Update Consent response + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + UPDATE_CONSENT_RESPONSE_EXPIRATION_DATE: + summary: Update Consent response with expiration date + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + /consents/retrieve-info: + post: + summary: Retrieve Consent Information + description: | + This operation allows the API Consumer to retrieve information about the Consent(s) for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The API Consumer can request that the texts intended for or previously shown to the User during the Consent Capture process for the requested scope(s) and Purpose be included in the response. If so, the `consentText` field will be included in the response for each matching Consent Information entry. + + The operation response may require more than one array item for the requested scope(s) and Purpose. For example, this may occur when the requested scopes relate to multiple APIs with independent User Consents. + + If the combination of the specified scope(s) and Purpose is permitted for the API Consumer but does not match any API(s) under Consent legal basis, an empty array will be returned. + operationId: retrieveConsentInfo + security: + - openId: + - consent-management:retrieve-info + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Accept-Language" + requestBody: + required: true + description: retrieveConsentInfo operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveConsentInfoRequestBody" + examples: + RETRIEVE_CONSENT_INFO_REQUEST: + summary: Retrieve Consent Information request + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestConsentText: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Language: + $ref: "#/components/headers/Content-Language" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveConsentInfoResponseBody" + examples: + RETRIEVE_CONSENT_INFO_PENDING: + summary: Retrieve Consent Information PENDING + description: Retrieve Consent Information when the User Consent is in PENDING status + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "PENDING" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_REQUESTED: + summary: Retrieve Consent Information REQUESTED + description: Retrieve Consent Information when the User Consent is in REQUESTED status + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "REQUESTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_DENIED: + summary: Retrieve Consent Information DENIED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "DENIED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_GRANTED: + summary: Retrieve Consent Information GRANTED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "GRANTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_EXPIRED: + summary: Retrieve Consent Information EXPIRED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "EXPIRED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2025-10-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_MULTIPLE_APIS: + summary: Retrieve Consent Information for multiple APIs + description: Retrieve Consent Information when the requested scopes relate to multiple APIs + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "GRANTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + - scopes: + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-654321" + consentStatus: "DENIED" + creationDate: "2025-08-15T10:00:00.000+02:00" + expirationDate: "2026-08-15T10:00:00.000+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with roaming verification for fraud prevention." + consentTextId: "pp-sha256-e5f6g7h8..." + lastUpdate: "2025-08-15T10:00:00.000+02:00" + RETRIEVE_CONSENT_INFO_EMPTY_ARRAY: + summary: Retrieve Consent Information with no matching API(s) under Consent legal basis + description: Retrieve Consent Information when there are no matching API(s) under Consent legal basis for the specified scope(s) and Purpose + value: [] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Consent403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Language: + description: | + The language of the response content, following the standard defined in [RFC 7231, Section 5.3.5](https://datatracker.ietf.org/doc/html/rfc7231#section-5.3.5) using language tags as defined by [BCP 47](https://tools.ietf.org/html/bcp47). + + This header may be included in the response to indicate the language used for the response content when the API Consumer supplies an `Accept-Language` request header. If supported, the API Provider should select the preferred language indicated in the `Accept-Language` header. If the `Accept-Language` header is not present in the request, this header may instead be included to specify the API Provider’s default response language. + schema: + $ref: "#/components/schemas/LanguageTags" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Accept-Language: + name: Accept-Language + in: header + description: | + The preferred language for the response content. It follows the standard defined in [RFC 7231, Section 5.3.5](https://datatracker.ietf.org/doc/html/rfc7231#section-5.3.5) using language tags as defined by [BCP 47](https://tools.ietf.org/html/bcp47). + + The `Accept-Language` header field can be used by API Consumers to indicate the set of natural languages that are preferred in the response. If not provided, it implies that the API Consumer will accept any language in response and the API Provider will use its default language for the response content. + schema: + $ref: "#/components/schemas/LanguageTags" + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + CreateConsentRequestBody: + type: object + description: | + The request body for the createConsent operation. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - consentStatus + - consentTextId + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + consentStatus: + $ref: "#/components/schemas/CreateConsentStatus" + consentTextId: + $ref: "#/components/schemas/ConsentTextId" + Scopes: + type: array + minItems: 1 + items: + type: string + description: | + List of requested scopes. The scope is a string that represents the access rights that the API Consumer is requesting from the User. + example: + - "location-verification:verify" + Purpose: + type: string + pattern: '^dpv:[a-zA-Z0-9]+$' + description: | + The reason for which personal data will be processed by the API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + example: "dpv:FraudPreventionAndDetection" + CreateConsentStatus: + type: string + description: | + The status of the User Consent being created. It must represent the final outcome resulting from the Consent Capture process with the User. The only allowed values are `GRANTED` and `DENIED` when creating a Consent. + + - `GRANTED`: The User has given their Consent to allow the requested data processing. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + enum: + - GRANTED + - DENIED + example: "GRANTED" + CreateConsentResponseBody: + type: object + description: The response body for the createConsent operation + required: + - consentId + - creationDate + properties: + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + UpdateConsentRequestBody: + type: object + description: | + The request body for the updateConsent operation. It allows updating the status of an existing User Consent. + properties: + consentStatus: + $ref: "#/components/schemas/UpdateConsentStatus" + UpdateConsentStatus: + type: string + description: | + The status of the User Consent being updated. The only allowed values are `GRANTED` and `DENIED` when updating a Consent. + + - `GRANTED`: The User has given their Consent to allow the requested data processing e.g. after previously denying it or when renewing an expired Consent. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + enum: + - GRANTED + - DENIED + example: "DENIED" + UpdateConsentResponseBody: + type: object + description: The response body for the updateConsent operation + required: + - consentId + - creationDate + properties: + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + RetrieveConsentInfoRequestBody: + type: object + description: | + The request body for the retrieveConsentInfo operation. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - requestConsentText + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + requestConsentText: + type: boolean + description: | + Indicates whether the texts intended for or previously shown to the User during the Consent Capture process for the requested scope(s) and Purpose should be included in the response. + + If set to `true`, the `consentText` field will be included in the response for each matching Consent Information entry. If set to `false`, the `consentText` field will be omitted from the response. + example: true + RetrieveConsentInfoResponseBody: + type: array + description: The response body for the retrieveConsentInfo operation + items: + $ref: "#/components/schemas/ConsentInfoItem" + ConsentInfoItem: + type: object + required: + - scopes + - purpose + - consentStatus + properties: + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + consentStatus: + $ref: "#/components/schemas/ConsentStatus" + consentText: + $ref: "#/components/schemas/ConsentText" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + ConsentStatus: + type: string + description: | + The status of the User Consent. The allowed values are: + + - `PENDING`: The User Consent is pending and has not yet been requested from the User. + - `REQUESTED`: The User Consent has been requested from the User, but the User has not yet responded. + - `GRANTED`: The User has given their Consent to allow the requested data processing. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + - `EXPIRED`: The User Consent has expired and is no longer valid. + enum: + - PENDING + - REQUESTED + - GRANTED + - DENIED + - EXPIRED + example: "GRANTED" + ConsentText: + type: object + description: | + The texts presented to the User during the Consent Capture process for the requested scope(s) and Purpose. + + It is composed of a title and a description, both of which are localized texts provided in the language indicated by the `Content-Language` response header (if present). There is also a unique, immutable string identifier, called a `consentTextId`, that designates a specific, versioned instance of a legal text. An optional `lastUpdate` timestamp can be included to indicate when the consent text version was last updated by the API Provider. + + These texts are only included in the response when explicitly requested by setting the `requestConsentText` field to `true` in the request. + required: + - title + - description + - consentTextId + properties: + title: + type: string + description: The localized text title + example: "Consent Required" + description: + type: string + description: The localized text description + example: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: + $ref: "#/components/schemas/ConsentTextId" + lastUpdate: + type: string + format: date-time + description: | + The date and time when this consent text version was last updated. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2025-07-03T14:27:08.312+02:00" + LanguageTags: + type: string + description: List of Language tags that identify natural languages, following [BCP 47](https://tools.ietf.org/html/bcp47) standard. + example: "en-US" + ConsentTextId: + type: string + description: | + This is a unique, immutable (e.g. hash-based) string identifier that designates a specific version of a legal text presented to the User during the Consent Capture process. + + The API consumer MUST submit this exact, unaltered identifier when creating a User Consent. + + This identifier creates a traceable, auditable link that binds a User's Consent to the specific textual content they were shown. + example: "pp-sha256-a1b2c3d4..." + CreationDate: + type: string + format: date-time + description: | + The date and time at which the User Consent was created. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2025-07-03T14:27:08.312+02:00" + ExpirationDate: + type: string + format: date-time + description: | + The date and time at which the validity of the User Consent is set to expire or has expired (when applicable). The API Provider determines the expiration date based on its internal policies. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2026-07-03T14:27:08.312+02:00" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Consent400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - CONSENT_MGMT.INVALID_CONSENT_TEXT_ID + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + INVALID_CONSENT_TEXT_ID: + description: The provided consentTextId does not match any valid consent text version available for the requested scope(s) and Purpose. + value: + status: 400 + code: CONSENT_MGMT.INVALID_CONSENT_TEXT_ID + message: The consentTextId provided is either invalid or does not exist. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Consent403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CONSENT_MGMT.NOT_ALLOWED_SCOPES_PURPOSE + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + NOT_ALLOWED_SCOPES_PURPOSE: + description: The requested scope(s) and Purpose combination is not allowed for the API Consumer, e.g. the API Consumer has not onboarded the appropriate API(s) with the API Provider for the declared Purpose. + value: + status: 403 + code: CONSENT_MGMT.NOT_ALLOWED_SCOPES_PURPOSE + message: The requested scope(s) and Purpose combination is not allowed for this API Consumer. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration +``` diff --git a/marked/ConsentManagement/documentation/API_documentation/README/raw.md b/marked/ConsentManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConsentManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ConsentManagement/documentation/SupportingDocuments/README/raw.md b/marked/ConsentManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ConsentManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/CustomerInsights/README/raw.md b/marked/CustomerInsights/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..dd301e614cacc91e032fde25e5e471869e1c3b9f --- /dev/null +++ b/marked/CustomerInsights/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# CustomerInsights + +Sandbox API Repository to describe, develop, document, and test the CustomerInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/owBuAQ) + +## Scope + +* Service APIs for “CustomerInsights” +* The API provides the customer with the ability to: + * Provides a risk index (a.k.a. Scoring) based on the individual's profile owned by a Telco Operator. + * So far two scoring scales are defined within the current proposal (GaugeMetric, VeritasIndex). +* Describe, develop, document, and test the APIs +* Started: October 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/CustomerInsights/releases/tag/r2.2) (Fall25), with the following API versions: + * **customer-insights v0.2.0** + [[YAML]](https://github.com/camaraproject/CustomerInsights/blob/r2.2/code/API_definitions/customer-insights.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CustomerInsights/r2.2/code/API_definitions/customer-insights.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CustomerInsights/r2.2/code/API_definitions/customer-insights.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CustomerInsights/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CustomerInsights/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CustomerInsights/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly on Thursdays at 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95737002367?password=034d9b74-a944-4def-ae30-0f93802430a5) + * Minutes: Access [[meeting minutes]](https://lf-camaraproject.atlassian.net/wiki/x/XIBuAQ) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/CustomerInsights/code/API_definitions/customer-insights/raw.md b/marked/CustomerInsights/code/API_definitions/customer-insights/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f8726d44ddb5ea9fb45a3d4d8ddb73713ddc6ce9 --- /dev/null +++ b/marked/CustomerInsights/code/API_definitions/customer-insights/raw.md @@ -0,0 +1,508 @@ +# customer-insights + +```yaml +openapi: 3.0.3 +info: + description: |- + Allows the API consumer to retrieve a risk index based on the individual's profile owned by a Telco Operator. + + # Relevant Definitions and concepts + + * **Scoring**: risk classification based on the individual's profile owned by a Telco Operator, i.e.: a rating on a scale that represents the risk index based on financial, socioeconomic and consumption data. + + Two different scales are considered for the Scoring: + + * **GaugeMetric**: Scoring scale that ranges from index 850 (lowest risk) to index 300 (highest risk), thus the higher the value of the index, the lower the risk it represents. This numerical scale is based on the globally recognized FICO score system. Values meaning is as follows: + + 800-850: Exceptional, very low risk. + + 740-799: Very Good, low risk. + + 670-739: Good, moderate risk. + + 580-669: Fair, higher risk. + + 300-579: Poor, very high risk. + + + * **VeritasIndex**: Scoring scale that ranges from index 0 (lowest risk) to index 19 (highest risk), thus the lower the value of the index, the lower the risk it represents. This numerical scale can be related with _alphabetical_ identifiers similar to those used by major rating agencies such as Standard & Poor's, Moody's and Fitch. Values meaning is as follows: + + 0-1 AAA + 2-3 AA + 4-5 A + 6-7 BBB + 8-9 BB + 10-11 B + 12-13 CCC + 14-15 CC + 16-17 C + 18-19 DDD + + # API Functionality + + This API allows to retrieve the Scoring information of a user within the operator. + + # Resources and Operations overview + + The API provides the following endpoint: + + - An operation to retrieve Scoring information. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Customer Insights + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/CustomerInsights +servers: + - url: "{apiRoot}/customer-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Scoring + description: Operations to retrieve Scoring information. +paths: + /scoring/retrieve: + post: + security: + - openId: + - customer-insights:scoring:read + tags: + - Scoring + summary: Retrieves Scoring information + description: >- + Retrieves Scoring information, for the user associated with the provided `idDocument`, `phoneNumber` or the combination of both parameters. + + It also allows to select the type of the Scoring scale measurement. + operationId: retrieveScoring + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ScoringRequest" + examples: + INPUT_GAUGE_METRIC: + summary: Gauge Metric + description: Gauge Metric score request, with no additional information. Default three-legged access mode for Gauge Metric + value: + scoringType: gaugeMetric + INPUT_VERITAS_INDEX: + summary: Veritas Index + description: Veritas Index score request, with no additional information. Default three-legged access mode for Veritas index + value: + scoringType: veritasIndex + INPUT_GAUGE_METRIC_PHONENUMBER: + summary: Gauge Metric with phoneNumber + description: Gauge Metric score request, with phoneNumber. Default two-legged access mode for Gauge Metric + value: + phoneNumber: "+556253423432" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_PHONENUMBER: + summary: Veritas Index with phoneNumber + description: Veritas Index score request, with phoneNumber. Default two-legged access mode for Veritas index + value: + phoneNumber: "+556253423432" + scoringType: veritasIndex + INPUT_GAUGE_METRIC_ID_DOCUMENT: + summary: Gauge Metric with idDocument + description: Gauge Metric score request, with idDocument. + value: + idDocument: "987654321" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_ID_DOCUMENT: + summary: Veritas Index with idDocument + description: Veritas Index score request, with idDocument. + value: + idDocument: "987654321" + scoringType: veritasIndex + INPUT_GAUGE_METRIC_PHONENUMBER_ID_DOCUMENT: + summary: Gauge Metric with phoneNumber and idDocument + description: Gauge Metric score request, with phoneNumber and idDocument. + value: + idDocument: "987654321" + phoneNumber: "+556253423432" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_PHONENUMBER_ID_DOCUMENT: + summary: Veritas Index with phoneNumber and idDocument + description: Veritas Index score request, with phoneNumber and idDocument. + value: + idDocument: "987654321" + phoneNumber: "+556253423432" + scoringType: veritasIndex + responses: + "200": + description: Scoring result. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ScoringResponse" + examples: + GAUGE_METRIC: + summary: Gauge Metric Response + description: Scoring with Gauge Metric index + value: + scoringType: gaugeMetric + scoringValue: 600 + VERITAS_INDEX: + summary: Veritas Index Response + description: Scoring with Veritas Index + value: + scoringType: veritasIndex + scoringValue: 4 + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + ScoringRequest: + type: object + properties: + idDocument: + type: string + description: |- + Identification number associated to the official identity document in the country. It may contain alphanumeric characters. + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scoringType: + type: string + description: |- + Scoring type, i.e.: scale. API Client may use this field to indicate the Scoring in one of the defined scales; if this field is not informed, the API will return the Scoring in the scale configured by default in the system. + + Allowed values are: + + * `gaugeMetric`: ranges from index 850 (lowest risk) to index 300 (highest risk) + * `veritasIndex`: ranges from index 0 (lowest risk) to index 19 (highest risk) + enum: + - gaugeMetric + - veritasIndex + ScoringResponse: + type: object + description: Scoring information based on the individual's profile owned by a Telco Operator. + required: + - scoringType + - scoringValue + properties: + scoringType: + type: string + description: |- + Scoring measurement system. + + Allowed values are: + + * `gaugeMetric`: ranges from index 850 (lowest risk) to index 300 (highest risk) + * `veritasIndex`: ranges from index 0 (lowest risk) to index 19 (highest risk) + enum: + - gaugeMetric + - veritasIndex + scoringValue: + type: integer + description: Result of the Scoring analysis expressed in the measure indicated in the `scoringType` field. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: |- + Problem with the client request. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + InvalidArgument: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: |- + Not found + + In addition to regular NOT_FOUND scenario, another scenarios may exist: + - Phone Number not found ("code": "IDENTIFIER_NOT_FOUND","message": "phoneNumber not found."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Generic422: + description: |- + Unprocessable Content + + In addition to regular scenario of Unprocessable Content, another scenarios may exist. + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + - Provided `scoringType` value is not supported. (`"code": "CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED","message": "Indicated parameter scoringType is not supported."`) + - Provided `idDocument` is not consistent with the phone number. (`"code": "CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS","message": "The request contains invalid data."`) + - Provided `idDocument` field is not supported. (`"code": "CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED","message": "Indicated parameter idDocument is not supported"`) + - Required `idDocument` field and it is not provided. (`"code": "CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED","message": "The idDocument is required to perform the properties validation."`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED + - CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS + - CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED + - CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + GENERIC_422_NOT_SUPPORTED_SCORING_TYPE_VALUE: + description: Error when `scoringType` value is not supported. + value: + status: 422 + code: CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED + message: Indicated parameter `scoringType` is not supported. + GENERIC_422_INVALID_IDENTIFIERS: + description: The request contains invalid data identifying customer + value: + status: 422 + code: CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS + message: The request contains invalid data. + GENERIC_422_ID_DOCUMENT_NOT_SUPPORTED: + description: Error when `idDocument` field is not supported + value: + status: 422 + code: CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED + message: Indicated parameter `idDocument` is not supported + GENERIC_422_ID_DOCUMENT_REQUIRED: + description: Error when `idDocument` field is not provided and it is required. + value: + status: 422 + code: CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED + message: The `idDocument` is required to perform the properties validation. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist/raw.md b/marked/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d0a6b23ff5f73a4b1b7063f0f26f734ad4101d6a --- /dev/null +++ b/marked/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Customer Insights v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference Information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/customer-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/customer-insights.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/customer-insights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/RYHWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/CustomerInsights/documentation/API_documentation/customer-insights-User-Story/raw.md b/marked/CustomerInsights/documentation/API_documentation/customer-insights-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8a7840a202766f19438324a6e2adbb2aefd482b4 --- /dev/null +++ b/marked/CustomerInsights/documentation/API_documentation/customer-insights-User-Story/raw.md @@ -0,0 +1,24 @@ +**User Story: Credit scoring service for banking** +
          + +| **Item** | **Details** | +| -------- | ----------- | +| ***Summary*** | As a bank officer, I want to evaluate a micro-credit application for a customer who has no credit history within our bank. I use the Customer Insights API to gather additional information about the customer's telco behavior to assess their creditworthiness. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
          **Actors:** Bank Officer, Bank System, Communication Service Provider (CSP)
          **Scope:** Retrieve a relevant score calculated from the data of the CSP, enabling the bank to make an informed decision on micro-credit approval. | +| ***Pre-conditions*** | The preconditions are listed below:
          1. The bank is integrated with the CSP's Customer Insights API.
          2. The customer has consented (3-legged scenarios) to sharing their telco data for credit assessment purposes.
          3. The bank officer has the necessary credentials to access the Customer Insights API.
          | +| ***Activities/Steps*** | **Begins when:** The bank officer submits a micro-credit application for a customer without an existing credit history.

          **Steps include:**
          1. The bank system makes a request to the Customer Insights API using customer consented information.
          2. The CSP processes the request and gathers telco-related behavioral insights.
          3. The CSP sends a calculated score to the bank system.
          4. The bank officer evaluates the score to assess the credit risk of the customer.

          **Ends when:** The bank officer either approves or declines the micro-credit application based on the insights provided. | +| ***Post-conditions*** | The bank officer has sufficient data to approve or deny the micro-credit request for a customer without a traditional credit history. | +| ***Exceptions*** | Several exceptions might occur during the Customer Insights API operations:
          - Unauthorized: Invalid credentials provided by the bank system.
          - Consent missing: The customer has not provided consent for sharing telco data (i.e. permission denied).
          - Data not found: Insufficient user data available for the customer.
          - Corporate customers: The API is not applicable for corporate customers. | + + +**User Story: Credit scoring service for riders** +
          + +| **Item** | **Details** | +| -------- | ----------- | +| ***Summary*** | As a service provider, I want to evaluate the creditworthiness of riders working for food delivery, errands, and other similar applications. I use the Customer Insights API to generate a score for these riders, which can be used by companies and banks to offer credit services to the riders for purchasing a motorcycle, bicycle, or electric scooter. The application can leverage the Customer Insights API to complement the score generated with additional telco data, enhancing the overall credit score. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
          **Actors:** Service Provider, Bank System, Rider, Application Service Provider (ASP), Communication Service Provider (CSP)
          **Scope:** Retrieve relevant behavioral data about the riders from both the delivery apps and the CSP, enabling a comprehensive credit score calculation to support credit decisions for vehicle purchases. | +| ***Pre-conditions*** | The preconditions are listed below:
          1. The service provider is integrated with both the delivery applications and the CSP's Customer Insights API.
          2. The rider has consented (3-legged scenarios) to share their delivery and telco data for credit assessment purposes.
          3. The service provider has the necessary credentials to access Customer Insights API and the path to route to the right CSP.
          | +| ***Activities/Steps*** | **Begins when:** The service provider initiates a credit assessment for a rider interested in purchasing a vehicle (motorcycle, bicycle, or electric scooter).

          **Steps include:**
          1. The service provider collects rider activity data from the delivery applications, including job completion rates, earnings, and overall performance.
          2. Optionally and out of the scope of CAMARA API, The service provider can make a request to other External Platforms API(s) available in the market (solution outside CAMARA, but to illustrate a real use case) using the collected data and rider consent details.
          3. The external ASP processes the request and generates a preliminary credit score based on the rider's delivery activities.
          4. The service provider then makes a request to the Customer Insights API to retrieve additional telco-related score about the rider.
          5. The CSP processes the request and gathers telco-related behavioral insights. The CSP sends a final enhanced credit score to the service provider.
          6. The service provider evaluates the received scores to assess the rider's creditworthiness for purchasing a vehicle.

          **Ends when:** The service provider either approves or declines the credit application based on the insights provided. | +| ***Post-conditions*** | The service provider has sufficient data to approve or deny the credit request for a rider based on a comprehensive score derived from both delivery app activity and telco data. | +| ***Exceptions*** | Several exceptions might occur during the Customer Insights API operations:
          - Unauthorized: Invalid credentials provided by the service provider.
          - Consent missing: The rider has not provided consent for sharing delivery or telco data (i.e. permission denied).
          - Data not found: Insufficient data available from delivery apps or telco records for the rider.
          - Corporate customers: The API is not applicable for corporate customers. | diff --git a/marked/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition/raw.md b/marked/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..531518ff51874a83385fbfb2a17a51fde857326f --- /dev/null +++ b/marked/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition/raw.md @@ -0,0 +1,107 @@ +# Algorithm Model Definition + +This document reflects the CAMARA WG Recommendation regarding the concepts to be evaluated for the implementation of the underlying algorithm for a specific scoring model. + +CAMARA WG recognizes this is a non-exhaustive list: +* This list can be enhanced from the learning and experience gained across different implementations +* An algorithm implementation is not required to support all the concepts listed below. Such a decision will be market by market case (i.e. country, by means of a consensus among Operators involved) + +The list of concepts is depicted below: + +| **ORDER (NOTE 1)** | **CONCEPT/PARAMETER (NOTE 2)** | **DESCRIPTION** | **FORMAT (NOTE 3)** | **ADDITIONAL COMMENTS** | **BASELINE CONCEPT (NOTE 4)**| +|:-------------------|:------------------------------:|:----------------|:-------------------:|:------------------------|:-----------------------------| +| #1 | subscription_type | Contract type (Postpay, Prepay, Control/Hybrid) | string | N/A | YES | +| #2 | customer_since_months | Time since the customer belongs to the Telco Operator in months | integer | N/A | YES | +| #3 | outgoing_calls_minutes_in_{period} | Accumulated time of outgoing calls in minutes in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #4 | outgoing_sms_in_{period} | Accumulated number of outgoing sms in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #5 | outgoing_data_{unit}_{subscription}\_in\_{period} | Accumulated outgoing data session in agreed {units}, {subscription} and {period} in the specific market:
          * {units}: MB or GB
          * {subscription}: Postpay, Prepay or Control/Hybrid (mixed case of Postpay/Prepay)
          * {period}: 1 month, 3 months, 6 months, ... | decimal | N/A | YES | +| #6 | incoming_calls_minutes_in_{period} | Accumulated time of incoming calls in minutes in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #7 | incoming_sms_in_{period} | Accumulated number of incoming sms in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #8 | arpu_in_{period} | Average revenue per user (ARPU), sometimes known as average revenue per unit, is a measure used primarily by consumer communications, digital media, and networking companies, defined as the total revenue divided by the number of subscribers in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES +| #9 | average_billing_amount_in_{period} | Average Billing Amount in the official market currency in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #10 | average_recharge_amount_in_{period} | Average Recharge Amount in the official market currency in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #11 | max_payment_due_date_delay_in_{period} | Maximum number of days the customer delayed his payment (after due date) in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...). Only applies to Postpay or Control/Hybrid | integer | N/A | NO | +| #12 | max_overdue_balance_in_{period} | Maximum balance amount in the official market currency that was not paid by due date over the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #13 | geographical_numbering_area | Geographical Numbering Area, representing the part of the phone number that is linked to a geographical (Fixed or Mobile Area). | integer | Used for instance in payments, when Telco Operator has the historical payments of customers and their ubication, in order to check number of payments and their amount (i.e. to check whether he/she is a good payer). | NO | +| #14 | social_net_data_{unit}_{subscription}\_in\_{period} | Accumulated outgoing data session consumed in Social Networks in agreed {units}, {subscription} and {period} in the specific market:
          * {units}: MB or GB
          * {subscription}: Postpay, Prepay or Control/Hybrid (mixed case of Postpay/Prepay)
          * {period}: 1 month, 3 months, 6 months, ... | decimal | This concept may have GDPR constraints in a given market to be considered. Please check regulation in the market/country for the consideration of this concept. | NO | + + +**NOTE 1**: This is a recommenadation for consideration order in the algorithm.
          +**NOTE 2**: This is an informative name, the exact name of the parameter is up to the implementation.
          +**NOTE 3**: This is a recommendation. Up to the implementation agreed in a specific market.
          +**NOTE 4**: This is a recommendation about which concepts (marked with YES) could be considered as potential baseline for initial implementations. The others (marked with NO) would be considered as advanced features.
          + +Below table shows the Telco Operator source system that hosts the above concepts: + +| **CONCEPT/PARAMETER** | **TELCO OPERATOR SOURCE SYSTEM** | +|:---------------------:|:---------------------------------| +| subscription_type | BSS | +| customer_since_months | BSS. Also related to [Tenure API functionality](https://github.com/camaraproject/Tenure) | +| outgoing_calls_minutes_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| outgoing_sms_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| outgoing_data_{unit}_{subscription}\_in\_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| incoming_calls_minutes_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| incoming_sms_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| arpu_in_{period} | BSS and CRM | +| average_billing_amount_in_{period} | OFCS and Billing System | +| average_recharge_amount_in_{period} | OCS | +| max_payment_due_date_delay_in_{period} | Billing System | +| max_overdue_balance_in_{period} | Billing System | +| geographical_numbering_area | HLR/HSS (Geographical Numbering Area may be part of the phoneNumber in some countries, e.g. Brazil Numbering +55**11**xxxxxxxx) | +| social_net_data_{unit}_{subscription}\_in\_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | + +LEGEND: +- BSS: Business Support Systems +- CRM: Customer Relationship Management +- HLR: Home Location Register +- HSS: Home Subscriber Server +- OCS: Online Charging System +- OFCS: Offline Charging System + + +## INFORMATIVE: Algorithm Model implementation examplification + +This section provides an example about how to the algorithm could be implemented. +The specific implementation approach in a given market MUST be discussed and agreed among involved participants (i.e. Telco Operators) in such a market. + +Below example considers: +- `veritasIndex` scoring +- postpay and prepay subscriptions in market +- period of 1 month +- data units in GB +- Indicated weight for each concept considered +- Concepts considered: The ones tagged as Baseline concepts (first eight ones) +- Example ranges for each concept associated to each score range + + +| **CONCEPT/PARAMETER** | **WEIGHT(%)** | **SCORE 0** | **SCORE 1** | **SCORE 2** | **SCORE 3** | **SCORE 4** | **SCORE 5** | **SCORE 6** | **SCORE 7** | **SCORE 8** | **SCORE 9** | **SCORE 10** | **SCORE 11** | **SCORE 12** |**SCORE 13** | **SCORE 14** | **SCORE 15** | **SCORE 16** | **SCORE 17** | **SCORE 18** | **SCORE 19** | +|:---------------------:|:----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:------------:|:------------:|:------------:|:-----------:|:------------:|:------------:|:------------:|:------------:|:------------:|:------------:| +| subscription_type | 12,5 | N/A | N/A | N/A | N/A | postpay | N/A | N/A | N/A | N/A | N/A | N/A | N/A | N/A | N/A | prepay | N/A | N/A | N/A | N/A | N/A | +| customer_since_months | 12,5 | x > 120 | 96 < x <= 120 | 72 < x <= 96 | 60 < x <= 72 | 48 < x <= 60 | 36 < x <= 48 | 24 < x <= 36 | 12 < x <= 24 | 11 < x <= 12 | 10 < x <= 11 | 9 < x <= 10 | 8 < x <= 9 | 7 < x <= 8 | 6 < x <= 7 | 5 < x <= 6 | 4 < x <= 5 | 3 < x <= 4 | 2 < x <= 3 | 1 < x <= 2 | 0 <= x <= 1 | +| outgoing_calls_minutes_in_{period} | 12,5 | x > 1140 | 1080 < x <= 1140 | 1020 < x <= 1080 | 960 < x <= 1020 | 900 < x <= 960 | 840 < x <= 900 | 780 < x <= 840 | 720 < x <= 780 | 660 < x <= 720 | 600 < x <= 660 | 540 < x <= 600 | 480 < x <= 540 | 420 < x <= 480 | 360 < x <= 420 | 300 < x <= 360 | 240 < x <= 300 | 180 < x <= 240 | 120 < x <= 180 | 60 < x <= 120 | 0 <= x <= 60 | +| outgoing_sms_in_{period} | 12,5 | > 100 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 35 < x <= 40 | 30 < x <= 35 | 25 < x <= 30 | 20 < x <= 25 | 17 < x <= 20 | 14 < x <= 17 | 12 < x <= 14 | 10 < x <= 12 | 8 < x <= 10 | 6 < x <= 8 | 4 < x <= 6 | 2 < x <= 4 | 0 <= x <= 2 | +| outgoing_data_{unit}_{subscription}\_in\_{period} | 12,5 | x > 160 | 150 < x <= 160 | 140 < x <= 150 | 130 < x <= 140 | 120 < x <= 130 | 110 < x <= 120 | 100 < x <= 110 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 30 < x <= 40 | 25 < x <= 30 | 20 < x <= 25 | 15 < x <= 20 | 10 < x <= 15 | 5 < x <= 10 | 0 <= x <= 5 | +| incoming_calls_minutes_in_{period} | 6,25 | x > 570 | 540 < x <= 570 | 510 < x <= 540 | 480 < x <= 510 | 450 < x <= 480 | 420 < x <= 450 | 390 < x <= 420 | 360 < x <= 390 | 330 < x <= 360 | 300 < x <= 330 | 270 < x <= 300 | 240 < x <= 270 | 210 < x <= 240 | 180 < x <= 210 | 150 < x <= 180 | 120 < x <= 150 | 90 < x <= 120 | 60 < x <= 90 | 30 < x <= 60 | 0 <= x <= 30 | +| incoming_sms_in_{period} | 6,25 | x > 57 | 54 < x <= 57 | 51 < x <= 54 | 48 < x <= 51 | 45 < x <= 48 | 42 < x <= 45 | 39 < x <= 42 | 36 < x <= 39 | 33 < x <= 36 | 30 < x <= 33 | 27 < x <= 30 | 24 < x <= 27 | 21 < x <= 24 | 18 < x <= 21 | 15 < x <= 18 | 12 < x <= 15 | 9 < x <= 12 | 6 < x <= 9 | 3 < x <= 6 | 0 <= x <= 3 | +| arpu_in_{period} | 25 | x > 190 | 180 < x <= 190 | 170 < x <= 180 | 160 < x <= 170 | 150 < x <= 160 | 140 < x <= 150 | 130 < x <= 140 | 120 < x <= 130 | 110 < x <= 120 | 100 < x <= 110 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 30 < x <= 40 | 20 < x <= 30 | 10 < x <= 20 | 0 <= x <= 10 | + + +**User A scenario score calculation** + +| **CONCEPT/PARAMETER** | **WEIGHT(%)** | **VALUE** | **MAPPED SCORE** | **WEIGHTED SCORE** | **SCORE** | +|:---------------------:|:-------------:|:---------:|:----------------:|:------------------:|:---------:| +| subscription_type | 12,5 | postpay | 4 | 0,5 | N/A | +| customer_since_months | 12,5 | 60 | 4 | 0,5 | N/A | +| outgoing_calls_minutes_in_{period} | 12,5 | 600 | 10 | 1,25 | N/A | +| outgoing_sms_in_{period} | 12,5 | 15 | 12 | 1,5 | N/A | +| outgoing_data_{unit}_{subscription}\_in\_{period} | 12,5 | 100 | 7 | 0,875 | N/A | +| incoming_calls_minutes_in_{period} | 6,25 | 300 | 10 | 0,625 | N/A | +| incoming_sms_in_{period} | 6,25 | 10 | 16 | 1 | N/A | +| arpu_in_{period} | 25 | 100 | 10 | 2,5 | N/A | +| scoringValue | 100% | N/A | N/A | 8,75 | 9 | + + +**scoringValue weighted score** is indicated in **column WEIGHTED SCORE** as the sum of the **WEIGHTED SCORE** of every concept.
          +**scoringValue** is indicated in **column SCORE** rounding to the nearest integer of the **scoringValue weighted score** + +NOTE: This example uses `,` as the decimal separator as per the `ISO 80000-1` standard. diff --git a/marked/CustomerInsights/documentation/SupportingDocuments/README/raw.md b/marked/CustomerInsights/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/CustomerInsights/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DedicatedNetworks/README/raw.md b/marked/DedicatedNetworks/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4a8e17e98a68a2aefd7f67fdec808b6610504b56 --- /dev/null +++ b/marked/DedicatedNetworks/README/raw.md @@ -0,0 +1,69 @@ + + + + + + + + + +# DedicatedNetworks + +Sandbox API Repository to describe, develop, document, and test the DedicatedNetworks Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/hAClB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XIArAQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/OICGAQ) + +For background on Dedicated Networks concepts and workflows, see the [General Description](documentation/API_documentation/DedicatedNetworks_GeneralDescription.md). + +## Scope + +* Service APIs for DedicatedNetworks (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API Consumer with the ability to: + * request/modify/delete a (logical) Dedicated Network for API consumers. + * A Dedicated Network offers + * specific connectivity performance (e.g. speed/ latency) + * during a specific time duration (e.g. one hour) and + * at specific locations (e.g. the area of a festival) + * A Dedicated Network may be ensured by an SLA. + * API consumers are able to manage access to this dedicated network for specific devices. +* Describe, develop, document, and test the APIs +* Started: October 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DedicatedNetworks/releases/tag/r1.2) (Fall25), with the following API versions: + * **dedicated-network-accesses v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network-accesses.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-accesses.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-accesses.yaml) + * **dedicated-network-profiles v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-profiles.yaml) + * **dedicated-network v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DedicatedNetworks/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DedicatedNetworks/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DedicatedNetworks/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: bi-weekly, Mondays, 10 AM CET (09:00 UTC). For date/time of the next meeting, see previous meeting minutes + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94505909302?password=67b9a175-154f-4fe1-986d-0b825227a95b) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/S3hQ1AFG) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using sp-cqm@lists.camaraproject.org. diff --git a/marked/DedicatedNetworks/code/API_definitions/dedicated-network-accesses/raw.md b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-accesses/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..882ce17d0a1f7e587b58ccdf62281b0de7964be8 --- /dev/null +++ b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-accesses/raw.md @@ -0,0 +1,966 @@ +# dedicated-network-accesses + +```yaml +openapi: 3.0.3 +info: + title: Dedicated Network - Accesses + description: | + + This API allows for requesting network access for devices. A device is identified by the CAMARA _device object_, containing either an MSIDSN or a Network Access Identifier. For more information about the Dedicated Networks APIs, see the _GeneralDescription_ document in the Dedicated Networks [repository](https://github.com/camaraproject/DedicatedNetworks/). + + A Device Access represents the permission for a specific device to use a Dedicated Network's reserved connectivity resources. Only devices for which a Device Access resource has been created can use the connectivity resources allocated for that network. The usage of resources can be tailored to each device within the constraints of the applicable Network Profile. + + A device is identified by the CAMARA `device` object, where at least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. + + Notes: + 1. Support for using an IP address as device identifier is not recommended when the IP address may change. The API invoker may not be able to associate the accesses resource with the targeted device anymore.
          Further, the device may be offline at time of Accesses API usage, thus, no IP address assigned. + 1. Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device`, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same `device` is identified by these two methods, as the server is unable to make this comparison. + - If the number of devices with access to the network is equal to or exceeds the 'maxNumberOfDevices', the API provider will provide a `429 QUOTA_EXCEEDED` error code. + + # Creating a device access + + A Device Access is created by performing a `POST` operation on the `/accesses` endpoint. + + The API Consumer provides the following information + + - the networkId to which access is being given + + - identifier of the device - either in `device` object or in the token (see "Identifying the device from the access token" above) + + - optionally, a default QoS Profile can be set for the device (see Network Profiles section in the dedicated-network-profiles API in the [Dedicated Networks repository](https://github.com/camaraproject/DedicatedNetworks/)). + + - optionally, a subset of QoS Profiles from this network can be provided to further restrict which QoS Profiles the device can access + + - Optionally, callback related information through sink and sinkCredential parameters to receive notifications about the lifecycle events of the device access. + + The API returns an accessId. The accessId is a unique identifier of the device access, which remains unchanged during its lifetime. The accessId is needed to query the status of the Device Access (GET /accesses/{accessId}) and to delete Access (DELETE accesses/{accessId}). + + Initially, the device access is in `REQUESTED` state. The device access is only usable when it is in `GRANTED` state. + + + ## Error handling: + + - If the dedicated network identified by the networkId is in an incompatible state when creating a device access, e.g. it is in the TERMINATED state, then the server will return an error with the `409 INCOMPATIBLE_STATE` error code. + + # Querying one or more device accesses + + All available device accesses of the API consumer can be queried by performing a `GET` operation on the `/accesses` endpoint. The query can be filted for accesses to a specific network (networkId) or for certain devices. + + A specific device access of the API consumer can be queried by performing a `GET` operation on the `/accesses/{accessId}` endpoint, where the accessId has been obtained during the _create_ procedure. + + # Deleting a device accesses + + A specific device access of the API consumer can be deleted by performing a `DELETE` operation on the `/accesses/{accessId}` endpoint. Deletion of the access can be interpreted as removal of the access permissions. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network-accesses/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Accesses + description: Manage accesses of devices for a dedicated network +paths: + + /accesses: + get: + tags: + - Accesses + summary: Get a list of device accesses to dedicated networks, optionally filtered for a given device and/or for a given dedicated network + operationId: listNetworkAccesses + security: + - openId: + - dedicated-network-accesses:accesses:read + parameters: + - name: networkId + in: query + description: Dedicated network id + schema: + $ref: '#/components/schemas/NetworkId' + - $ref: "#/components/parameters/x-device" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of existing device accesses to dedicated networks, optionally filtered for a given device and/or for a dedicated network (the list can be empty) + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkAccessInfo' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + post: + tags: + - Accesses + summary: Create a device access to a dedicated network with given configuration + description: | + **NOTE:** + - When the API allows usage of a two-legged access token and the invoker uses it, the optional `device` object shall be present. + operationId: createNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateNetworkAccess' + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Device access status callback + summary: "Device access status notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + It will be called upon change of the network access request status. + Currently only DEVICE_ACCESS_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + '201': + description: Successful creation of network access for a device + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkAccessInfo' + headers: + Location: + description: 'URL including the resource identifier of the newly created network access.' + required: true + schema: + type: string + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /accesses/{accessId}: + get: + tags: + - Accesses + summary: Get a device access to the dedicated network and its configuration + operationId: readNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:read + parameters: + - name: accessId + in: path + required: true + schema: + $ref: "#/components/schemas/AccessId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: A device access to the dedicated network with configuration + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkAccessInfo' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Accesses + summary: Delete a device access to the dedicated network + operationId: deleteNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:delete + parameters: + - name: accessId + in: path + required: true + schema: + $ref: "#/components/schemas/AccessId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Successful deletion of a device access + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + x-device: + name: x-device + in: header + description: Device object represented in a header + Device object (#/components/schemas/Device") represented in a header. + It is serialized according to RFC 8941 as a structured field value where + the Device object is a dictionary, with the following additonal provisions + - property names are changed to lower case to comply with the RFC + - serializing property values must comply with the RFC depending on the type, and in particular + - if the property value is a string which contains only ASCII characters, the string can be serialized as String, + as per section 3.3.3 of the RFC + - if the property value is a string and contains non-ASCII characters, the string must be serialized as Byte Sequence using UTF-8 encoding, + as per section 3.3.5 of the RFC + schema: + type: string + example: 'phonenumber="+123456789"' + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + AccessId: + description: Network access id in UUID format + type: string + format: uuid + + NetworkId: + description: Network id in UUID format + type: string + format: uuid + + DeviceAccessStatus: + description: | + The current status of the device access. The status can be one of the following: + * `REQUESTED` - The Device Access is requested, but not granted. Possible transitions to GRANTED and DENIED states + * `GRANTED` - The Device Access is granted by the CSP, and the device can access the Dedicated Network when the network is in the ACTIVATED state. Possible transition to DENIED state + * `DENIED` - The Device Access is denied by the CSP, and the device can not access the Dedicated Network. The denial can be caused by a veriaty of conditions, such as lack of resources or system failure. + + type: string + enum: + - REQUESTED + - GRANTED + - DENIED + + ReasonInfo: + type: object + required: + - code + - message + properties: + code: + type: string + description: A human-readable code to describe the reason + message: + type: string + description: A human-readable description of what the reason represents + + DeviceAccessStatusInfo: + description: Additional information about the reason for the current device access status + type: object + properties: + reason: + allOf: + - $ref: "#/components/schemas/ReasonInfo" + - type: object + properties: + code: + enum: + - REQUEST_APPROVED + - REQUEST_REJECTED + - REQUEST_FAILED + - ACCESS_REVOKED + - ACCESS_FAILED + + BaseNetworkAccessInfo: + description: Common attributes of a device access to a dedicated network + type: object + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + device: + $ref: "#/components/schemas/Device" + qosProfiles: + description: (Optional) List of supported QOS profiles usable for the device. When absent, all QosProfiles of the Network are supported. Only a subset of the QOS profiles of the network is allowed + type: array + items: + type: string + minItems: 1 + defaultQosProfile: + description: (Optional) The default QOS profile of a device access. When absent, the defaultQosProfile of the Network is used + type: string + sink: + description: The address to which events shall be delivered using the selected protocol. + type: string + format: uri + pattern: ^https:\/\/.+$ + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + required: + - networkId + + CreateNetworkAccess: + description: Attributes required to create a dedicated network access for a device. + # NOTE this design prepares for adding request specific attributes later + allOf: + - $ref: "#/components/schemas/BaseNetworkAccessInfo" + + NetworkAccessInfo: + description: Information about a dedicated network access for a device + allOf: + - $ref: "#/components/schemas/BaseNetworkAccessInfo" + - type: object + properties: + id: + $ref: "#/components/schemas/AccessId" + status: + $ref: "#/components/schemas/DeviceAccessStatus" + statusInfo: + $ref: "#/components/schemas/DeviceAccessStatusInfo" + required: + - id + - status + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.dedicated-network.v0.device-access-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.dedicated-network-accesses.v0.device-access-status-changed: "#/components/schemas/EventDeviceAccessStatusChanged" + + EventDeviceAccessStatusChanged: + description: Event to notify a device access status change + type: object + properties: + data: + type: object + description: Status change details + required: + - accessId + - deviceAccess + properties: + accesskId: + $ref: "#/components/schemas/AccessId" + status: + $ref: "#/components/schemas/DeviceAccessStatus" + statusInfo: + $ref: "#/components/schemas/DeviceAccessStatusInfo" + required: + - data + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + - INCOMPATIBLE_STATE + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + GENERIC_409_INCOMPATIBLE_STATE: + description: A resource referenced in the request is in an incompatible state for the requested operation + value: + status: 409 + code: INCOMPATIBLE_STATE + message: A referenced resource is in an incompatible state. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + + DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE: + summary: Device access status changed + description: Cloud event example for network status change to GRANTED + value: + id: 625b2d4b-4da7-4f07-9169-e60ffdf7667c + source: 'https://api.example.com/dedicated-network-accesses/v0/accesses/b69e5404-3871-448d-8f9f-11dc5d29a4c8' + specversion: '1.0' + type: "org.camaraproject.dedicated-network.v0.device-access-status-changed" + time: '2024-11-29T13:04:00Z' + data: + accessId: b69e5404-3871-448d-8f9f-11dc5d29a4c8 + status: GRANTED + statusInfo: + code: REQUEST_APPROVED + message: The device access request is approved. +``` diff --git a/marked/DedicatedNetworks/code/API_definitions/dedicated-network-areas/raw.md b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-areas/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b2243aef0cc22828eee9d50eca50087099aa6aa7 --- /dev/null +++ b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-areas/raw.md @@ -0,0 +1,437 @@ +# dedicated-network-areas + +```yaml +openapi: 3.0.3 +info: + title: Dedicated Network - Areas + description: | + + # Introduction + + This API allows for discovering available network service areas, which are the geographical areas offered by the network provider where consitent coverage according to indicated network profile(s) and QoS profiles is provided, and which is to be used in conjunction with the Dedicated Network API. + + For more information about the Dedicated Network APIs, see the _GeneralDescription_ document in the Dedicated Networks [repository](https://github.com/camaraproject/DedicatedNetworks/). + + # Network Service Areas + + A Network Service Area represents a geographical area with coverage consistent with the characteristics of the network profiles and the QoS profiles supported in the area. It enables API Consumers to select the geographical area where they can expect to consume the reserved network connectivity resources. A Network Service Area may have been pre-agreed between the API Provider and API Consumer. + + A Network Service Area contains information about its geographical boundaries and the supported network profiles and QoS profiles. It is uniquely identified by a UUID identifier and it contains a human readable name and description. + + # Network Service Areas API + + The key characteristics of the API include: + + - Network Service Areas are read-only resources from the API Consumer perspective + + - They are discoverable by POST operations + + - They are readable by GET operations + + - Each Network Service Area has a unique identifier (areaId) + + - The areaId serves as a reference when creating a Dedicated Network + + - The API returns only Network Service Areas that the API Consumer is eligible to use based on their agreements + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Querying one or more Areas + + All available network service areas of the API consumer can be queried by performing a `POST` operation on the `/retrieve-service-areas` endpoint. + + The API Consumer may provide the following input parameters as search criteria which must be matched for the network service area to be returned: + + - `atLocation` - to return the network service areas available at the given geographical location + + - `overlappingArea` - to return the network service areas whose geographical area overlaps (but does not fully cover) the input geographical area, where the input geographical area may be a circle or polygon + + - `coveringArea` - to return the network service areas whose geographical area fully covers the input geographical area will be returned, where the input geographical area may be a circle or polygon + + - `byName` - to return the network service areas with a name matching exactly the input string + + - `byNetworkProfileId` - to return the network service areas which support the input network profile identifier + + - `byQosProfileName` - to return the network service areas which support the input QoS profile name + + A specific network service area of the API consumer can be queried by performing a `GET` operation on the `/areas/{areaId}` endpoint. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +servers: + - url: "{apiRoot}/dedicated-network-areas/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /retrieve-service-areas: + post: + tags: + - Areas + summary: Retrieve dedicated network service areas, filtered by additional search criteria + operationId: retrieveNetworkServiceAreas + requestBody: + description: Parameters to query service areas + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveServiceAreasRequest" + required: true + responses: + '200': + description: List of available dedicated network service areas + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/ServiceArea' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + /areas/{areaId}: + get: + tags: + - Areas + summary: Read a dedicated network service area + operationId: readNetworkServiceArea + parameters: + - name: areaId + in: path + required: true + schema: + $ref: "#/components/schemas/ServiceAreaId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Information about the dedicated network service area + content: + application/json: + schema: + $ref: '#/components/schemas/ServiceArea' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkProfileId: + type: string + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ServiceAreaId: + type: string + format: uuid + + RetrieveServiceAreasRequest: + description: Request object to retrieve service areas that match all the given properties + type: object + properties: + atLocation: + $ref: "#/components/schemas/Point" + overlappingArea: + $ref: "#/components/schemas/Area" + coveringArea: + $ref: "#/components/schemas/Area" + byName: + type: string + byNetworkProfileId: + $ref: "#/components/schemas/NetworkProfileId" + byQosProfileName: + $ref: "#/components/schemas/QosProfileName" + + ServiceArea: + description: Common attributes of a service area, i.e. where the dedicated network service is supported + properties: + id: + $ref: '#/components/schemas/ServiceAreaId' + name: + type: string + description: + type: string + area: + $ref: '#/components/schemas/Area' + networkProfiles: + description: Dedicated network profiles which are supported in this area. + type: array + items: + $ref: "#/components/schemas/NetworkProfileId" + minItems: 1 + qosProfiles: + description: Qos Profiles which are supported in this area. + type: array + items: + $ref: '#/components/schemas/QosProfileName' + minItems: 1 + required: + - id + - area + anyOf: + - required: + - networkProfiles + - required: + - qosProfiles + + Area: + description: Common attributes of a geographical area, base schema for all area types + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + description: | + Radius from `center` in meters. + minimum: 1 + maximum: 200000 + required: + - center + - radius + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map. + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location. + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location. + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. +``` diff --git a/marked/DedicatedNetworks/code/API_definitions/dedicated-network-profiles/raw.md b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-profiles/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4e512e9ab62d869f281d44679cff93d8a3fc2442 --- /dev/null +++ b/marked/DedicatedNetworks/code/API_definitions/dedicated-network-profiles/raw.md @@ -0,0 +1,406 @@ +# dedicated-network-profiles + +```yaml +openapi: 3.0.3 +info: + title: Dedicated Network - Network Profiles + description: | + + # Introduction + + This API allows for discovering available network profiles, which are offered by the network provider to be used in conjunction of the Dedicated Network API. Network profiles describe the capabilities and performance targets of a dedicated network. For more information about the Dedicated Networks APIs, see [link](). + + # Network Profiles + + A Network Profile represents a predefined set of network capabilities and performance characteristics that can be applied when creating a Network. It enables API Consumers to understand the capabilities they can expect when using the reserved network connectivity resources. A Network Profile is a validated, supported configuration that has been pre-approved between the API Provider and API Consumer. + + A Network Profile contains information about the maximum number of devices allowed, the aggregated throughput to be provided, and a set of allowed QoS Profiles that devices can use when having access to the Dedicated Network. The concept of named QoS Profiles is re-used from the [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) API family. An API provider may offer the QualityOnDemand `qos-profiles` API for resolving a QoS Profile name into characteristics of a specific QoS profile. + + Network Profiles are designed to support different use-cases and should contain the matching `qos-profile` combinations. Generally, two types of Network Profiles can be identified + * Network Profiles containing only a `defaultQosProfile` + * Network Profiles containing one or more additional `qos-profile`s with the `qosProfiles` array. When multiple QoS Profiles are supported within one Network Profile, the QualityOnDemand `quality-on-demand` API may be used to assign one of the available QoS profiles to a specific device while the Network is in `ACTIVATED` state + + Devices are not neccessarily using connectivity continuously. The value of the `maxNumberOfDevices` parameter should be set _generous_, considering that not all devices using connectivity simultaneously and/or continuously. + + The parameters `aggregatedUlThroughput` and `aggregatedDlThroughput` define the (hard) limits of simultaneous connectivity usage, ie. sum of all traffic pertaining all devices using the available QoS profiles. + + A detailed description of the individual parameters may be included within the _terms and conditions_ (outside of scope for the API). + + # Network Profiles API + + The key characteristics of the API include: + + - Network Profiles are read-only resources from the API Consumer perspective + + - They are discoverable through GET operations + + - Each Network Profile has a unique identifier (profileId) + + - The profileId serves as a reference when creating a Dedicated Network + + - The API returns only Network Profiles that the API Consumer is eligible to use based on their agreements + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network-profiles/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /profiles: + get: + tags: + - Profiles + summary: Read dedicated network profiles + operationId: readNetworkProfiles + security: + - openId: + - dedicated-network-profiles:profiles:read + parameters: + - name: name + in: query + description: name of a network profile + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of available network profiles + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkProfile' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /profiles/{profileId}: + get: + tags: + - Profiles + summary: Read a dedicated network profile + operationId: readNetworkProfile + security: + - openId: + - dedicated-network-profiles:profiles:read + parameters: + - name: profileId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkProfileId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of available network profiles + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkProfile' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkProfileId: + description: Network profile id in UUID format + type: string + format: uuid + + NetworkProfile: + type: object + properties: + id: + $ref: '#/components/schemas/NetworkProfileId' + name: + description: A human-readable name to describe the network profile + type: string + maxNumberOfDevices: + type: integer + aggregatedUlThroughput: + $ref: "#/components/schemas/BitRate" + aggregatedDlThroughput: + $ref: "#/components/schemas/BitRate" + qosProfiles: + description: Qos Profiles, which are supported by the dedicated network. + type: array + items: + $ref: '#/components/schemas/QosProfileName' + minItems: 1 + defaultQosProfile: + $ref: '#/components/schemas/QosProfileName' + required: + - id + - maxNumberOfDevices + - aggregatedUlThroughput + - aggregatedDlThroughput + - qosProfiles + - defaultQosProfile + + BitRate: + description: Specification of bitrate + type: object + properties: + value: + description: Quantity of bitrate + type: integer + example: 10 + format: int32 + minimum: 1 + maximum: 1024 + unit: + $ref: "#/components/schemas/BitRateUnitEnum" + + BitRateUnitEnum: + description: Units of bitrate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. +``` diff --git a/marked/DedicatedNetworks/code/API_definitions/dedicated-network/raw.md b/marked/DedicatedNetworks/code/API_definitions/dedicated-network/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c36011afb7e8c3f26620bcf963fd3b3cbdd5110a --- /dev/null +++ b/marked/DedicatedNetworks/code/API_definitions/dedicated-network/raw.md @@ -0,0 +1,706 @@ +# dedicated-network + +```yaml +openapi: 3.0.3 +info: + title: Dedicated Network - Networks + description: | + This API allows for requesting a Dedicated Network, which provides a set of capabilities and connectivity performance targets. The Dedicated Network may be requested for a particular geographical location and at a particular time window. Depending on the requested start time for the dedicated network, the network may first enter a _reserved_ state. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Creating a network + + A network is created by performing a `POST` operation on the `/networks` endpoint. + + The API Consumer needs to provide the following input parameters to create a network: + + - the chosen Network Profile (networkProfileId) or QoS profile (qosProfileName). The choice is between a Network Profile (which contains properties like maximum number of devices, aggregated throughput, a list of supported QOS profiles, and a default QoS profile) and a QoS Profile which is equivalent to a simplified Network Profile for a single device, with just a default QoS profile, and with the aggregated throughput corresponding to the throughput defined by the QoS Profile. + + - the Service Area (serviceAreaId) + + - the service start and end times (Service Time). + + - Optionally, callback related information through sink and sinkCredential parameters to receive notifications about the lifecycle events of the network. + + The API returns a networkId. The networkId is a unique identifier of the network, which remains unchanged during its lifetime. The networkId is required when creating Device Accesses. + + Initially, the created network is in `REQUESTED` state. The network is only usable when the network is in `ACTIVATED` state. Find a detailed description of the network states [here](). + + + # Querying one or more Networks + + All available network of the API consumer can be queried by performing a `GET` operation on the `/networks` endpoint. + + A specific network of the API consumer can be queried by performing a `GET` operation on the `/networks/{networkId}` endpoint, where the networkId has been obtained during the _create_ procedure. + + # Deleting a Network + + A specific network of the API consumer can be deleted by performing a `DELETE` operation on the `/networks/{networkId}` endpoint. Deletion of a network can be interpreted as a cancellation of the resource reservation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Networks + description: Manage a dedicated network +paths: + /networks: + get: + tags: + - Networks + summary: Get a list of dedicated networks + operationId: listNetworks + security: + - openId: + - dedicated-network:networks:read + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of dedicated networks (the list can be empty) + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkInfo' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + post: + tags: + - Networks + summary: Request to create a dedicated network + operationId: createNetwork + security: + - openId: + - dedicated-network:networks:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateNetwork' + parameters: + - $ref: "#/components/parameters/x-correlator" + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Network status callback + summary: "Network status notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + It will be called upon change of the network request status. + Currently only NETWORK_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + NETWORK_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/NETWORK_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + '201': + description: Reception acknowlegement a dedicated network request + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkInfo' + headers: + Location: + description: 'URL including the resource identifier of the newly created dedicated network.' + required: true + schema: + type: string + format: uri + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /networks/{networkId}: + get: + tags: + - Networks + summary: Get the current information about a dedicated network + operationId: readNetwork + security: + - openId: + - dedicated-network:networks:read + parameters: + - name: networkId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Current dedicated network information + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkInfo' + '400': + $ref: "#/components/responses/Generic400" + '404': + $ref: "#/components/responses/Generic404" + delete: + tags: + - Networks + summary: Delete a dedicated network + operationId: deleteNetwork + security: + - openId: + - dedicated-network:networks:delete + parameters: + - name: networkId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Successful deletion of a dedicated network + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network id in UUID format + type: string + format: uuid + + NetworkProfileId: + description: Network profile id in UUID format + type: string + format: uuid + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ServiceAreaId: + type: string + format: uuid + + BaseNetworkInfo: + description: Common attributes of a dedicated network + type: object + properties: + networkProfileId: + $ref: '#/components/schemas/NetworkProfileId' + qosProfileName: + $ref: '#/components/schemas/QosProfileName' + serviceTime: + $ref: '#/components/schemas/ServiceTime' + serviceAreaId: + $ref: '#/components/schemas/ServiceAreaId' + sink: + description: The address to which events shall be delivered using the selected protocol. + type: string + format: uri + pattern: ^https:\/\/.+$ + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + required: + - serviceTime + - serviceAreaId + oneOf: + - required: + - networkProfileId + - required: + - qosProfileName + + NetworkInfo: + description: Current dedicated network information + allOf: + - $ref: "#/components/schemas/BaseNetworkInfo" + - type: object + properties: + id: + $ref: '#/components/schemas/NetworkId' + status: + $ref: '#/components/schemas/NetworkStatus' + required: + - id + - status + + CreateNetwork: + description: Attributes required to create a dedicated network + # NOTE this design prepares for adding request specific attributes later + allOf: + - $ref: "#/components/schemas/BaseNetworkInfo" + + NetworkStatus: + description: | + The current status of the requested network. The status can be one of the following: + * `REQUESTED` - The DN is requested, but not approved. Possible transitions to RESERVED, ACTIVATED and TERMINATED states + * `RESERVED` - Request is accepted by the CSP (CSP has committed the requested resources), but the Network cannot be used (outside of requested time-window) + * `ACTIVATED` - Network turns from reserved into Activated. Now, devices with access can use the network. Possible transitions to RESERVED or TERMINATED states + * `TERMINATED` - The Network resource is used and up for deletion. The API does not allow any action (except delete). + + type: string + enum: + - REQUESTED + - RESERVED + - ACTIVATED + - TERMINATED + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.dedicated-network.v0.network-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.dedicated-network.v0.network-status-changed: "#/components/schemas/EventNetworkStatusChanged" + + EventNetworkStatusChanged: + description: Event to notify a network status change + type: object + properties: + data: + type: object + description: Status change details + required: + - networkId + - status + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + status: + $ref: "#/components/schemas/NetworkStatus" + required: + - data + + ServiceTime: + type: object + properties: + start: + type: string + format: date-time + description: It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + end: + type: string + format: date-time + description: It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + required: + - start + - end + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + examples: + + NETWORK_STATUS_CHANGED_EXAMPLE: + summary: Network status changed + description: Cloud event example for network status change to ACTIVATED + value: + id: 625b2d4b-4da7-4f07-9169-e60ffdf7667c + source: 'https://api.example.com/dedicated-network/v0/networks/b69e5404-3871-448d-8f9f-11dc5d29a4c8' + specversion: '1.0' + type: "org.camaraproject.dedicated-network.v0.network-status-changed" + time: '2024-11-29T13:04:00Z' + data: + networkId: 'b69e5404-3871-448d-8f9f-11dc5d29a4c8' + status: 'ACTIVATED' +``` diff --git a/marked/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription/raw.md b/marked/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..40410d043633ed5c8bdd03604ae958b647146d8f --- /dev/null +++ b/marked/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription/raw.md @@ -0,0 +1,241 @@ +# High level description of Dedicated Networks concept and APIs +## Introduction +_Dedicated Networks_ enable dedicated use of public network connectivity resources by reserving some of these resources for use by devices and applications. To these devices and applications, the reserved resources appear as their own virtual or logical network. Please check [here](https://github.com/camaraproject/DedicatedNetworks/blob/r1.1/documentation/SupportingDocuments/UsageScenarios.md) for several usage scenarios for Dedicated Networks. + +Fixed and Mobile Networks already offer the capability of separating devices into different networks. These concepts are sometimes called logical networks or virtual private networks. Multiple of these networks can coexist on the same physical network and can separate target traffic from other traffic for assured performance, enhanced security and other scenarios where consistent experience is required. + +There are different options to technically realize a Dedicated Network. For example: + +- Using 5G Network Slices (see 3GPP 23.501 Rel-15, clause 5.15) + +- Using 5G Non-Public Networks (NPN), specifically the Public Network Integrated NPN (PNI-NPN), see 3GPP 23.501 Rel-16, clause 5.30) + +- Using a separate 4G APN (see 3GPP 23.401 Rel-8) or 5G DNNs (see 3GPP 23.501 Rel-15). Note, a DNN is equivalent to an APN, per 3GPP 23.003 Rel-15. + +Dedicated Networks abstract the complexity across **Network Provider** realizations to enable coherent use of diverse network capabilities. + +A Dedicated Network is often only needed for a specific time duration (e.g. one hour) and at specific locations (e.g. the area of a festival). These are referred to as Service Time and Service Area. + +The CAMARA Dedicated Network APIs allow **API Consumers** to programmatically manage Dedicated Networks, without the need for in-depth knowledge of telecommunications systems. + +API Consumers have control over which devices are allowed to access and use the reserved network connectivity resources. In addition, network connectivity characteristics, for example, routing and performance may be individually tailored for each device. + +Detailed characteristics, behaviors and costs pertaining to Dedicated Networks are typically described by the **API Provider** in the terms and conditions. Such terms and conditions may also contain obligations and restrictions. + +An API Provider realizes Dedicated Networks based on the physical network resources managed by a Network Provider. An API Provider can be the Network Provider. + +The present set of [Usage Scenarios](../SupportingDocuments/UsageScenarios.md) focuses on B2B use-cases, where the owner of the devices / device subscriptions is also acting as API invoker for the Networks and the Accesses APIs. This constellation allows using using the MSISDN as device identifier with a two-legged access tokens, since no additional consent needs to be obtained. + + +**Key roles** + +| **Role Name** | **Description** | +| ---- | ------- | +| API Consumer | The entity that consumes the Dedicated Network APIs | +| API Provider | The entity that provides the Dedicated Network APIs | +| Network Provider | The entity that provides the physical network resources | + +## Dedicated Network APIs + +The CAMARA Dedicated Network APIs allow for programmatic management of Dedicated Networks, without the need for in-depth knowledge of telecommunications systems. + +The APIs are summarized in the table below followed by a brief description. Detailed descriptions are provided within each specification. + +| **API** | **Purpose of the API** | **Key Abstractions and concepts** | +| ---- | ------- | ----| +| Dedicated Network API | Reservation and lifecycle management of network connectivity resources for dedicated use. | A Dedicated Network is a logical resource and is used to embody the reservation of network connectivity resources in the physical network. Initiating a new reservation request using this API results in a new Dedicated Network resource being created. The Dedicated Network undergoes various lifecycle States including REQUESTED, RESERVED, ACTIVATED and TERMINATED. Reservation of resources occurs based on the selected Network Profile, duration when the reservation is needed (Service Time) and geographical areas where the service is needed (Service Area). | +| Dedicated Network Profiles API | Discovery of predefined set of network capabilities and performance characteristics | A Network Profile represents a predefined set of network capabilities and performance characteristics that can be applied when creating dedicated networks. Each profile represents a validated, supported configuration that has been pre-approved in the _terms and conditions_ between the API Provider and API Consumer. | +| Dedicated Network Areas API | Discovery of network service areas with support for network profiles and QoS profiles | A Network Service Area represents a geographical area with coverage consistent with one or more network profiles and/or one or more QoS profiles. It enables API Consumers to select the geographical area where they can expect to consume the reserved network connectivity resources. A Network Service Area may have been pre-agreed between the API Provider and API Consumer in the _terms and conditions_ between the API Provider and API Consumer. | +| Dedicated Network Accesses API | Managing access to the Dedicated Network, i.e., controlling which devices may benefit from the reserved resources and capabilities | A Device Access represents the permission for a specific device to use a Dedicated Network's reserved connectivity resources. The usage of resources can be tailored to each device within the constraints of the applicable Network Profile.
          The access for devices to the network can only be managed when the Network is created and not in the TERMINATED [state](#states-of-the-network). | + +The Accesses and the Network Profile re-use the concept of named QoS Profiles from [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) for describing connectivity performance characteristics. An API provider may offer the `qos-profiles` API for resolving a QoS Profile name into characteristics of a specific QoS profile. + +When multiple QoS profiles are defined within a Network Profile, the API Consumer may either statically assign a different QoS profile (from the set of QoS profiles) for each device access or may dynamically create QoS Sessions using the QualityOnDemand `quality-on-demand` API. +The API Consumer may also restict the list of possible QoS Profiles within a Device Access. + +A high-level sequence of steps involved when using Dedicated Network APIs is depicted in the diagram below and further described in their respective sections. + +**Figure**: High-level sequence of steps
          + +```mermaid + graph TD + 0[Complete Pre-requisites] + 1[Choose Dedicated Network Service Area] + A[Choose Dedicated Network Profile or QoS Profile] + B[Create a Dedicated Network] + C[Create Device Accesses] + D[Allowed devices can use reserved network connectivity resources] + 0 --> 1 + 1 --> A + A --> B + B --> C + C --> D +``` + +## Pre-requisites + +Before Dedicated Network APIs can be invoked, relevant agreements need to be in place between the API Consumer and the API Provider. Conceptually, the agreement contains all the different terms and conditions, which typically include price, service descriptions and conditions. It also includes obligations and restrictions possibly for both, the API Provider and the API Consumer, etc. + +An API Provider may provide a catalog where API Consumers can get an overview of the various options available. For example, there may be a catalog of available APIs, and a catalog of available parameter sets for each of the APIs. + +The API Provider may also offer a procedure for requesting additional customization, for example, additional Service Areas or Network Profiles. Such a procedure can leverage conventional methods such as emails or phone conversations. + +API Consumers selects from available Network Profiles, QoS profiles, and Service Areas offered by the API Provider which then become part of the agreed terms and conditions. + +This preparation phase is **outside the scope** of the Dedicated Network APIs. + +As result of the agreement on the terms and conditions, the following aspects are determined + +- URLs and credentials for the API Consumer to use + +- A set of capabilities and performance targets (Network Profiles and QoS Profiles) that an API Consumer is eligible to use + +- A set of geographic areas (Service Areas) that an API Consumer is eligible to use + +- The API Consumer is aware about the terms and conditions (incl price), when selecting different parameter or parameter combinations according to the conditions. + +Note that, at completion of the pre-requisites, no network connectivity resources are reserved, i.e., no Dedicated Network is created. + +## Detailed high-level flow +The diagram below attempts to depict the complete flow including API endpoint, response codes, and key parameters. + +**Figure**: High Level Flow with additional details +```mermaid + +sequenceDiagram + participant App as API Consumer (Application) + participant P as Profiles API + participant A as Areas API + participant N as Networks API + participant A as Accesses API + participant Network as Physical Network + participant D as Device(s) + Note over App,D: Pre-requisites completed + + rect rgba(51, 49, 49, 0.6) + note right of App: 1: Reading Profiles + App->>P: GET /profiles + P->>App: 200 OK (Profiles [profileId, ...]) + end + + rect rgba(51, 49, 49, 0.6) + note right of App: 2: Discovering Areas + App->>P: POST /retrieve-service-areas + P->>App: 200 OK (Service areas [areaId, ...]) + end + + rect rgba(51, 49, 49, 0.6) + note right of App: 3: Creating a Dedicated Network + App->>N: POST /networks (profileId or qosProfileName, areaId, serviceTime, ...) + N->>App: 201 Created (networkId, status=REQUESTED, ...) + N <<-->> Network: Provisioning / configuration as needed
          Managed by API Provider and Network Provider
          Outside scope of the Dedicated Network APIs + alt Callback enabled + N-->>App: Optional callback: (networkId, status=RESERVED) + N-->>App: Optional callback: (networkId, status=ACTIVATED) + else Polling + App->>N: GET /networks/{networkId} + N-->>App: 200 OK (networkId, status=ACTIVATED) + end + end + rect rgba(51, 49, 49, 0.6) + note right of App: 4: Managing Device Access + loop Create Access resource for a given device to the given network + App->>A: POST /accesses (networkId, device) + A->>App: 201 Created (accessId, status=REQUESTED) + end + alt Callback enabled + N-->>App: Optional callback: (accessId, status=GRANTED) + else Polling + App->>N: GET /accesses/{accessId} + N-->>App: 200 OK (accessId, status=GRANTED) + end + A <<-->> Network: Provisioning / configuration as needed
          Managed by API Provider and Network Provider
          Outside scope of the Dedicated Network APIs + loop Delete a previously created Access resource + App->>A: DELETE /accesses (accessId) + A->>App: 204 No Content + end + end + Note over App,D: 4: Dedicated Network in ACTIVATED state + loop One or more devices in GRANTED state + D-->>Network: Connect to network + Network-->>D: Connection established / denied + end +``` + +Description of main steps +1. Reading Profiles: The API Consumer is reading the eligible Network Profiles. Each Network Profile contains properties, like aggregated throughput or QoS profiles. Reading of the eligible QoS Profiles may also occur in this step (not shown in the diagram). + * The terms and conditions (see [Pre-requisites](#pre-requisites)) may define the conditions, constrains, etc for using the profile. +1. Discovering Areas: The API Consumer is retrieving the eligible Network Service Areas. Each Network Service Area contains properties, like the areas's geographical coordinates and supported network profiles and QoS profiles. + * The terms and conditions (see [Pre-requisites](#pre-requisites)) may define the conditions, constrains, etc for using the service area. +1. Creating a Dedicated Network: The API Consumer creates a network, providing the network profile or QoS profile, service time and service area as input parameters + * The network is initially in REQUESTED state. See [network lifecycle](#states-of-the-network) for more information. + * The API Consumer can register a sink for receiving network state changes. +1. Managing Device Access: The API Consumer may allow one or more devices to get access to the capabilities and pcapacity of the network + * The API Consumer may use the Accesses API, while the network is either in REQUESTED, RESERVED or ACTIVATED state. The API Consumer gets an error code, when using the Accesses API with a Network in TERMINATED state. + * Creating an Access resource corresponds to giving access for a device to the network. + * Deleting an Access resource corresponds to revoking access for a device to the network. +1. When Dedicated Network is in ACTIVATED state: Devices with access will be able to connect to the network. + * When a single QoS profile is used or a default QoS profile is defined within the Network Profile (or changed via the Access resources), all the traffic of the device will be treated with this QoS profile as default + * When multiple QoS profiles are defined within the Network Profile (or changed via the Access resources), the API Consumer may use the QOD API for managing QoS Sessions with the QoS Profiles listed in the Network Profile. + +## States of the network + +The dedicated network supports multiple states, i.e. REQUESTED, RESERVED, ACTIVATED and TERMINATED. The networks resource is created with a POST on the /networks API. The status of the HTTP resource is independent of the status of the representing dedicated network. + +On successful acceptance of the request, an HTTP resource is created. The response always returns a REQUESTED State. Reserved resources are only usable when the network is in ACTIVATED state. + +**Figure**: lifecycle of a network + +```mermaid +stateDiagram-v2 + [*] --> REQUESTED: POST /networks + REQUESTED --> RESERVED: Use is confirmed (Service Time not reached) + RESERVED --> ACTIVATED: Service Time reached + ACTIVATED --> TERMINATED: Service Time expires + REQUESTED --> ACTIVATED: Use is confirmed (Service Time already reached) + RESERVED --> TERMINATED: Failed to reserve resources +``` + +Explainations +- A network in REQUESTED state is not (yet) committed by the Network Provider. + +- A network in RESERVED state is committed to be available for use during the Service Time by the Network Provider. + +- The targeted resources of the network are free to be used by other users or for other purposes, while the network is in RESERVED state. + +- Reserved resources are only usable when the network is in ACTIVATED state. + +- The network may enter the ACTIVATED state directly after the REQUESTED state if the service start time has been reached when the API Provider successfully completed the resource reservation. + +- The network may enter the TERMINATED state directly after the REQUESTED state if the API Provider could not complete the resource reservation. + +- A network in TERMINATED state cannot be modified anymore and should be deleted. If not deleted by the API Consumer, the representing HTTP resource (URL) may be removed by the API Provider. + +## States of device access to the network + +The device access to the dedicated network supports multiple states, i.e. REQUESTED, GRANTED, and DENIED. The networks access resource is created with a POST on the /accesses API. It contains `deviceAccess` object which contains the state information of the device access. + +On successful acceptance of the request, an HTTP resource is created. The response always returns a REQUESTED State. Reserved resources are only usable when the network is in ACTIVATED state. + +**Figure**: lifecycle of a device access to network + +```mermaid +stateDiagram-v2 + [*] --> REQUESTED: POST /accesses + REQUESTED --> GRANTED: Device Access is granted + REQUESTED --> DENIED: Device Access is rejected or it failed + GRANTED --> DENIED: Device Access is revoked (after having been granted) or it failed. +``` + +Explainations +- A device access is usable only when it is in GRANTED state while the dedicated network is in ACTIVATED state. + +- A device access will transition from REQUESTED to GRANTED state (with reason code: REQUEST_APPROVED) when the access to the network is approved. + +- A device access will transition from REQUESTED to DENIED state (with reason code: REQUEST_FAILED) if failure occured while approving the request. + +- A device access will transition from REQUESTED to DENIED state (with reason code: REQUEST_REJECTED) if the request is rejected. + +- A device access will transition from GRANTED to DENIED state (with reason code: ACCESS_FAILED) if failure occured after the access has been granted. + +- A device access will transition from GRANTED to DENIED state (with reason code: ACCESS_REVOKED) when the grant to access the network is revoked. diff --git a/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist/raw.md b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..18fbb6cc0994526b250c3fa2e6c8054bcd61f3b7 --- /dev/null +++ b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network.yaml](/code/API_definitions/dedicated-network.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist/raw.md b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0ab25ba97fc6d5836c3704e7bd26c90a99fea76c --- /dev/null +++ b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network-accesses v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network-accesses.yaml](/code/API_definitions/dedicated-network-accesses.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist/raw.md b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..453627e46aea3c64c06b8f819705bbf6b728f67d --- /dev/null +++ b/marked/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network-profiles v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network-profiles.yaml](/code/API_definitions/dedicated-network-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DedicatedNetworks/documentation/SupportingDocuments/README/raw.md b/marked/DedicatedNetworks/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DedicatedNetworks/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios/raw.md b/marked/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..047921aca8b9b286b0d7ecb43ebd64302cb67f3b --- /dev/null +++ b/marked/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios/raw.md @@ -0,0 +1,60 @@ +# Usage Scenarios of the Dedicated Networks API + +## Introduction + +The API was motivated by a number of use cases and usage scenarios during the API presentation ([pdf](https://github.com/camaraproject/APIBacklog/blob/main/documentation/SupportingDocuments/DedicatedNetworks%C2%A0API%C2%A0Introduction.pdf)). A short description is provided in the following. + +## Media Production + +A Media Producer needs a stable connectivity performance for a camera crew with two or more cameras for capturing the live video footage of a press briefing event. Although multiple cameras are actively used during the production, only a single live video stream is produced. The different cameras are positioned to capture different aspects of the press briefing, for example, one camera is capturing all speakers (pan view) and another camera is capturing individual speakers (head and shoulder). The program director selects the camera (called “Live Camera”), which is feeding the outgoing live video stream. For the selection, the video stream of each camera is shown at a production gallery to the production director. + +Each camera should get the needed connectivity performance (in terms of throughput) during the press briefing event. Standby Cameras (cameras, which are only streaming the video to the production gallery) can have a lower quality and lower QOS. The live camera (camera, which is currently feeding the outgoing video stream) should have a higher quality and higher QOS. The used QOS profile is changed dynamically for each camera. + +The media producer is planning the video production of the press briefing before the press briefing event. It should be assumed that the media producer is already an API customer of the Network Provider and has access to the Dedicated Network API. The Network is prepared with the needed configurations, like QOS Profile configurations. + +The media producer decides on the used cameras before the press briefing. It should be assumed that the media producer has access to a pool of cameras, including video encoding and transmission equipment, and only a subset of cameras are used within a certain production event. Each camera is equipped with a matching SIM for the Network Provider. The media producer permits devices (SIMs), which should get access to the capabilities provided by the Dedicated Network. + +## Festival + +The festival organizer is interested in obtaining a dedicated network from a public network provider to connect multiple devices for “running” a festival. Thus, the dedicated network is not intended for the festival audience/visitors. The stable connectivity performance provided by the dedicated network is needed for operating credit card readers (festival payment system) and for the CCTV (security) cameras. The quality of the CCTV cameras can be switched between “matrix view” (low quality for each camera) and “single view” (high quality for the single camera). An according QOS profile is selected as needed. + +The festival organizer is planning the festival, e.g., how many credit card readers & CCTV cameras are needed. The festival organizer knows, “where” (location) and “when” (time) the festival will be and is interested in getting a dedicated network for enabling the festival. + +It should be assumed that the festival organizer is already an API customer of the Network Provider and has access to the Dedicated Network API. Each device is equipped with a matching SIM for the Network Provider. It should be assumed that the festival organizer has more devices/SIMs and only uses a subset of these devices. The festival organizer permits devices (SIMs), which should get access to the capabilities provided by the Dedicated Network. + +## Enterprise + +A dedicated network is used to connect devices (e.g., Laptops) of employees to corporate services. Different connectivity quality (QOS Profiles) is needed, e.g., during a video conference/virtual meeting. During a virtual meeting, one or more meeting participants may decide to switch on the video camera in addition to the audio streams, to improve the meeting quality. + +The Enterprise wants secure access to its corporate services and is planning the needed capacity. The devices are managed by the enterprise IT organization. It should be assumed that the enterprise is already an API customer of the Network Provider, which offers the Dedicated Network API. Each device is equipped with a matching SIM for the Network Provider. The enterprise permits only its own devices (SIMs) to get access to the capabilities provided by the Dedicated Network. + +## Additional Scenarios + +Here are the other Dedicated Network use cases they can be added to the list: + +- **Emergency Services**: Dedicated Networks provide reliable communication and data services for emergency responders, ensuring they have the necessary information and connectivity during critical situations. + +- **Smart Cities**: Dedicated Networks support intelligent transport systems, public safety, and other smart city applications. +The following use cases from 3-12 can be added under the Enterprise section. + +- **Airports**: Dedicated Networks can be used for video surveillance, asset tracking, and real-time data analytics to enhance security and operational efficiency. + +- **Mining**: In the mining industry, Dedicated Networks support remote control of machinery, environmental monitoring, and predictive maintenance. + +- **Manufacturing and Logistics**: Dedicated Networks enable the use of Automated Guided Vehicles (AGVs), robots, and drones for efficient operations. They also support asset tracking and real-time data analytics. + +- **Ports**: Dedicated Networks facilitate the management of logistics and supply chains, ensuring smooth operations and tracking of assets. + +- **Oil & Gas**: Dedicated Networks are used for environmental monitoring, asset tracking, and ensuring safety in operations. + +- **Utilities**: Dedicated Networks support the monitoring and management of utility services, enhancing reliability and efficiency. + +- **Rail**: Dedicated Networks are used for asset tracking, remote control of machinery, and real-time data analytics to improve safety and efficiency in rail operations + +- **Healthcare**: In hospitals, Dedicated Networks ensure secure and reliable connectivity for life-saving systems and medical devices. + +- **Public Venues**: In large public venues like stadiums and convention center's, Dedicated Networks provide predictable connectivity and enhanced security for various applications. + +- **Industrial Applications**: Dedicated Networks support robotics, automated inventory control, and other industrial applications that require constant connectivity and low latency. + +- **Transportation and Logistics**: Dedicated Networks facilitate the tracking and management of assets, ensuring efficient operations in transportation and logistics. \ No newline at end of file diff --git a/marked/DeviceAuthenticity/README/raw.md b/marked/DeviceAuthenticity/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8894d793b4c9ded1cdadc55f84bce10fca2e2490 --- /dev/null +++ b/marked/DeviceAuthenticity/README/raw.md @@ -0,0 +1,43 @@ + + + + + + + + + +# DeviceAuthenticity + +Sandbox API Repository to describe, develop, document, and test the DeviceAuthenticity Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/czLe) + +## Scope + +* Service API(s) “DeviceAuthenticity” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * Determine whether a given device associated with the provided device identifier is subject to any restrictions or risk flags. + * Provide a clear overall status describing the device’s condition. +* Describe, develop, document, and test the API(s) +* Started: **December 2025** + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually together with the DeviceIdentifier API team + + * Schedule: First Friday of each month at 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96981252767?password=fc957607-cc06-450f-b80a-229bb6a88c39) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/yjve) +* Mailing List (of DeviceIdentifier) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS/raw.md b/marked/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..59d23b056cb98a329061a96e33143f4c0249ed24 --- /dev/null +++ b/marked/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS/raw.md @@ -0,0 +1,522 @@ +# IMEI-FRAUD-OAS + +```yaml +openapi: 3.0.3 +info: + title: IMEI Fraud Check + version: wip + description: | + # Summary + + The IMEI Fraud Check API allows clients to verify the status of mobile devices using their IMEI (International Mobile Equipment Identity) across three operator-managed registers: allowed lists, prohibited lists, and tracked lists. + + This API is useful for various scenarios: + - Device registration and network access control + - Insurance claims validation - verify if a claimed lost/stolen device is actually prohibited + - Device purchase verification - check if a second-hand device has a clean status + - Fraud prevention - detect potentially fraudulent devices before service activation + - Compliance with regulatory requirements for device management + - Network monitoring and tracking of specific devices + + # Introduction + + The International Mobile Equipment Identity (IMEI) is a unique identifier assigned to mobile devices by manufacturers. This 15-digit number serves as a fingerprint for each device and is used by mobile networks to identify equipment on their networks. + + Mobile operators maintain three distinct registers for IMEI management: + + ## Register Types + + ### Allowed List (White List) + Contains all number series of equipment identities that are permitted for use on the network. Devices on this list are explicitly authorized for network access. + + ### Prohibited List (Black List) + Contains all equipment identities that belong to equipment that must be barred from network access. This includes devices that are: + - **Lost**: Device reported missing by the subscriber + - **Stolen**: Device reported stolen by the subscriber or law enforcement + - **Blacklisted**: Device blocked due to fraud, non-payment, or other policy violations + - **Blocked**: Device restricted from network access for regulatory or technical reasons + + ### Tracked List (Gray List) + Contains equipment identities that are monitored by the network for evaluation or other purposes. Devices on the tracked list are not barred from network access (unless they are also on the prohibited list or not on the allowed list), but their network activity is logged and monitored. + + The use of these registers is at the operators' discretion, and the specific implementation may vary between different network operators and jurisdictions. + + # Relevant terms and definitions + + ### IMEI Fraud Check API service endpoint + The URL pointing to the RESTful resource of the IMEI Fraud Check API. + + ### International Mobile Equipment Identity (IMEI) + A unique 15-digit identifier assigned to mobile devices by the manufacturer, used to identify the device on mobile networks. + + ### Register Status + The classification of a device based on its presence in operator-maintained registers (allowed, prohibited, tracked lists). + + ### Device Status + The operational status of a device on the network, determined by evaluating its presence across all applicable registers. + + # API functionality + + The API defines one primary service endpoint: + + - `POST /check-status` to verify the register and operational status of a device using its IMEI + + To call this endpoint, the API consumer must first obtain a valid access token from the token endpoint, which is then passed as an Authorization header. The API consumer must provide the IMEI of the device to be checked in the request body. + + If the request is valid, the API response is a JSON object containing the device status and register information: + - The response will always contain `imei` and `operationalStatus`. + - A `lastChecked` field indicates when the information was last verified + - If the device has a negative status, `reportedDate` and `prohibitedReason` may be included if available + - Other response parameters are implementation dependent + + An example of a JSON response object is as follows: + ``` + { + "lastChecked": "2024-02-20T10:41:38.657Z", + "imei": "490154203237518", + "operationalStatus": "prohibited", + "prohibitedReason": "stolen", + "reportedDate": "2023-05-23T21:48:42.000Z" + } + ``` + + ## Status Determination Logic + + The operational status is determined based on register presence: + 1. If the device is on the **prohibited list**: status is "prohibited" (regardless of other lists) + 2. If the device is on the **allowed list** and not on prohibited list: status is "allowed" + 3. If the device is only on the **tracked list**: status is "tracked" + 4. If the device is not on any list: status is "unknown" + + ## Error handling + + Errors may be returned for the following reasons. Note that this list is not exhaustive. + + `401 UNAUTHENTICATED`: + - The access token is not a valid access token for the API provider + - The access token was valid but has now expired + + `400 INVALID_ARGUMENT`: + - The API request is not compliant with this OAS definition + - Invalid IMEI format provided + + `400 OUT_OF_RANGE`: + - A parameter value in the API request is outside the documented range + + `404 IDENTIFIER_NOT_FOUND`: + - The IMEI provided in the request is not found in any accessible database + + `403 PERMISSION_DENIED`: + - The access token does not have the required scope for the endpoint being called + + `422 SERVICE_NOT_APPLICABLE`: + - The IMEI fraud check service cannot be applied to the provided identifier + + `429 QUOTA_EXCEEDED`: + - The API consumer has exceeded their allocated quota for this API + + `429 TOO_MANY_REQUESTS`: + - The rate limit for API requests has been exceeded + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 + + +servers: + - url: "{apiRoot}/imei-fraud-check/vwip" + variables: + apiRoot: + default: https://api.example.com + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: IMEI Fraud Check + description: Check the register status of mobile devices using their IMEI + +paths: + "/check-status": + post: + summary: Check the register status of a device using its IMEI + description: Verify if an IMEI is present in allowed, prohibited, or tracked lists maintained by operators + operationId: checkImeiStatus + tags: + - IMEI Fraud Check + security: + - openId: + - imei-fraud-check:check-status + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: IMEI to be checked for register status + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Check IMEI Status: + $ref: '#/components/examples/CheckImeiStatus' + + responses: + "200": + $ref: '#/components/responses/200CheckStatus' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs. The OpenID Connect discovery URL will be provided by the API provider during onboarding. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + 200CheckStatus: + description: IMEI register status has been successfully retrieved + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/ImeiStatus" + examples: + Allowed IMEI: + description: IMEI status check for an allowed device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237518" + operationalStatus: "allowed" + Prohibited IMEI (Stolen): + description: IMEI status check for a prohibited device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237519" + operationalStatus: "prohibited" + prohibitedReason: "stolen" + reportedDate: "2023-05-23T21:48:42.000Z" + Tracked IMEI: + description: IMEI status check for a tracked device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237520" + operationalStatus: "tracked" + Unknown IMEI: + description: IMEI status check for a device not in any register + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237521" + operationalStatus: "unknown" + Multi-Register IMEI: + description: IMEI present in multiple registers (prohibited takes precedence) + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237522" + operationalStatus: "prohibited" + prohibitedReason: "blacklisted" + reportedDate: "2023-08-15T14:30:22.000Z" + + 400BadRequest: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Invalid IMEI Format: + description: IMEI format is invalid + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid IMEI format. IMEI must be 15 digits." + Missing IMEI: + description: IMEI parameter is missing + value: + status: 400 + code: INVALID_ARGUMENT + message: "IMEI is required" + + 401Unauthorized: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated Request: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + 403Forbidden: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permission Denied: + description: Access token does not have required scope + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + 404NotFound: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + IMEI Not Found: + description: The provided IMEI is not found in any database + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The provided IMEI cannot be found in any accessible database. + + 422UnprocessableContent: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + Service Not Applicable: + description: The fraud check service is not applicable for this IMEI + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The fraud check service is not applicable for the provided IMEI. + + 429TooManyRequests: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + Too Many Requests: + description: Rate limit exceeded + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached + Quota Exceeded: + description: API quota exceeded + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota + + schemas: + CommonResponseBody: + description: Common parameters included in all responses + properties: + lastChecked: + description: | + Date and time that the information was last confirmed by the fraud check service to be correct. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ImeiStatus: + description: The register and operational status information for the queried IMEI + type: object + properties: + imei: + type: string + description: The IMEI that was checked + pattern: '^[0-9]{15}$' + example: "490154203237518" + operationalStatus: + type: string + description: The operational status of the device, determined by register presence + enum: + - allowed + - prohibited + - tracked + - unknown + example: "allowed" + prohibitedReason: + type: string + description: Reason why the IMEI is prohibited. Only included when operationalStatus is "prohibited". + enum: + - lost + - stolen + - blacklisted + - blocked + - fraud + - non-payment + - regulatory + example: "stolen" + reportedDate: + type: string + format: date-time + description: | + Date and time when the IMEI was reported with its current prohibited status (only present when operationalStatus is "prohibited"). It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-05-23T21:48:42.000Z" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the error represents + + RequestBody: + description: Request body for IMEI register status check + type: object + required: + - imei + properties: + imei: + type: string + description: The IMEI number of the device to check (15 digits) + pattern: '^[0-9]{15}$' + example: "490154203237518" + + XCorrelator: + type: string + pattern: '^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$' + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + examples: + CheckImeiStatus: + description: Example request to check IMEI register status + value: + imei: "490154203237518" +``` diff --git a/marked/DeviceAuthenticity/code/API_definitions/README/raw.md b/marked/DeviceAuthenticity/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/DeviceAuthenticity/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/DeviceAuthenticity/documentation/API_documentation/README/raw.md b/marked/DeviceAuthenticity/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceAuthenticity/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceAuthenticity/documentation/SupportingDocuments/README/raw.md b/marked/DeviceAuthenticity/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceAuthenticity/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceDataVolume/README/raw.md b/marked/DeviceDataVolume/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0393e5d2f3f02e28a54306d4d87b91da92793b25 --- /dev/null +++ b/marked/DeviceDataVolume/README/raw.md @@ -0,0 +1,56 @@ + + + + + + + + + +# DeviceDataVolume + +Sandbox API Repository to describe, develop, document, and test the DeviceDataVolume APIs within the Sub Project [DeviceStatus](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/PoCaBQ) + +## Scope + +* Service APIs “Device Data Volume” and "Device Data Volume Subscriptions" (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The service APIs provide the customer with the ability to: + * get detailed insights into the customer's data usage status + * get alerts when the customer's data usage status changes +* Describe, develop, document, and test the service APIs +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/DeviceDataVolume/releases/tag/r1.3) (Fall25), with the following API versions: + * **device-data-volume-subscriptions v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceDataVolume/blob/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml) + * **device-data-volume v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceDataVolume/blob/r1.3/code/API_definitions/device-data-volume.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceDataVolume/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceDataVolume/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceDataVolume/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings for the DeviceStatus Sub Project are held virtually + * Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions/raw.md b/marked/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..562e5f4801ad89c5442ad58dbfc7a8ca55a04317 --- /dev/null +++ b/marked/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions/raw.md @@ -0,0 +1,1715 @@ +# device-data-volume-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Data Volume Subscriptions + description: | + This API enables customers to subscribe to events related to data volume usage thresholds on a device. It supports both request and subscription modes to track remaining data volume. + + # Introduction + + ## Device Data Volume Subscriptions + + API consumers can receive notifications regarding data volume usage thresholds, such as when the remaining data volume reaches 50%, 75%, or 90% of the user's allocated data plan. This is useful for managing data usage and avoiding overage fees. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity capable of network communication, identified via an IP address, phone number, or Network Access Identifier. + + # API Functionality + + The API exposes the following capabilities: + + ## Device Data Volume Subscriptions + + These endpoints allow management of subscriptions to data volume usage events. The CAMARA subscription model follows the CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` related to data volume thresholds you wish to track. + + The following event `types` are managed for this API: + - `org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent`: Event triggered when 50% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent`: Event triggered when 75% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent`: Event triggered when 90% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded`: Event triggered when the data plan is exceeded. + + Note: Additionally, the following events could be send, which do not require a dedicated subscription: + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding device data volume events can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceDataVolume + +servers: + - url: "{apiRoot}/device-data-volume-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Device Data Volume Subscriptions + description: Manage subscriptions to device data volume usage events. + +paths: + /subscriptions: + post: + tags: + - Device data volume subscription + summary: "Create a device data volume event subscription" + description: Create a subscription for data volume usage events + operationId: createDeviceDataVolumeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Data Volume server will call this endpoint whenever a data volume usage event occurs. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + data-50-percent: + $ref: "#/components/examples/DATA_50_PERCENT" + data-75-percent: + $ref: "#/components/examples/DATA_75_PERCENT" + data-90-percent: + $ref: "#/components/examples/DATA_90_PERCENT" + data-exceeded: + $ref: "#/components/examples/DATA_EXCEEDED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Successful Subscription Creation: + $ref: "#/components/examples/SUBSCRIPTION_CREATION" + Successful Subscription Creation With Device Disambiguation: + $ref: "#/components/examples/SUBSCRIPTION_CREATION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Device data volume subscription + summary: "Retrieve a list of device data volume subscriptions" + description: Retrieve a list of data volume usage event subscription(s) + operationId: retrieveDeviceDataVolumeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-data-volume-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + examples: + Subscription List: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty Subscription List: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device data volume subscription + summary: "Retrieve a device data volume event subscription" + description: Retrieve a specific subscription by ID + operationId: retrieveDeviceDataVolumeSubscription + security: + - openId: + - device-data-volume-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device data volume subscription + summary: "Delete a device data volume event subscription" + operationId: deleteDeviceDataVolumeSubscription + description: | + This operation deletes a specific data volume usage subscription by its subscription ID. + Once deleted, no more notifications will be sent for the corresponding subscription. + security: + - openId: + - device-data-volume-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: No Content - Subscription successfully deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now. + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential for authentication, containing an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier (e.g., username). + type: string + secret: + description: The secret (e.g., password). + type: string + + AccessTokenCredential: + type: object + description: An access token credential for authentication. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: A previously acquired token for accessing the resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: Expiry time for the access token. + accessTokenType: + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetail: + description: The details of the requested device data volume subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + Subscription: + description: Represents a device data volume subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address where events will be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription for device data volume. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + id: + $ref: "#/components/schemas/SubscriptionId" + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionEventType: + type: string + description: | + Event types that can be triggered for device data volume monitoring. + enum: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + format: uuid + description: Unique identifier for the subscription. + example: 550e8400-e29b-41d4-a716-446655440000 + + NotificationEventType: + type: string + description: | + data-50-percent - Event triggered when the device reaches 50% data usage thresholds of the data plan used. + + data-75-percent - Event triggered when the device reaches 75% data usage thresholds of the data plan used. + + data-90-percent - Event triggered when the device reaches 90% data usage thresholds of the data plan used. + + data-exceeded - Event triggered when the device reaches 100% data usage exceeded of the data plan used. + + subscription-started: Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription is terminated. + enum: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-started + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + - data + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + example: sd5e-uy52-88t4-za66 + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/NotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent: "#/components/schemas/EventDataUsage50Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent: "#/components/schemas/EventDataUsage75Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent: "#/components/schemas/EventDataUsage90Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded: "#/components/schemas/EventDataUsageExceeded" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have a time zone. + example: "2018-04-05T17:31:00Z" + + # Event structures for data volume + EventDataUsage50Percent: + description: Event structure for data usage 50% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsage75Percent: + description: Event structure for data usage 75% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsage90Percent: + description: Event structure for data usage 90% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsageExceeded: + description: Event structure for data usage exceeding the allocated volume + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: Event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: | + Event detail structure for org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended event. + Note that the device object is defined as optional and will only to be returned if provided in createSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createSubscription). + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_UNPROCESSABLE - Subscription cannot be processed due to some reason. Useful for asynchronous subscription creation. + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_UNPROCESSABLE + - SUBSCRIPTION_EXPIRED + - SUBSCRIPTION_DELETED + - ACCESS_TOKEN_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: SUBSCRIPTION_MISMATCH + message: Inconsistent access token for requested events subscription + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + DATA_50_PERCENT: + value: + id: "124007" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1406" + time: "2024-05-12T12:45:23.682Z" + + DATA_75_PERCENT: + value: + id: "124008" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1407" + time: "2024-05-12T14:30:23.682Z" + + DATA_90_PERCENT: + value: + id: "124009" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1408" + time: "2024-05-12T16:15:23.682Z" + + DATA_EXCEEDED: + value: + id: "124010" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1409" + time: "2024-05-12T18:00:23.682Z" + + SUBSCRIPTION_STARTED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ENDED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_CREATION: + description: A new subscription has been successfully created + value: + protocol: HTTP + protocolSettings: + method: POST + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + config: + subscriptionDetail: {} + subscriptionExpireTime: '2023-01-17T13:18:23.682Z' + subscriptionMaxEvents: 5 + initialEvent: true + id: 550e8400-e29b-41d4-a716-446655440000 + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + SUBSCRIPTION_CREATION_WITH_DEVICE_DISAMBIGUATION: + description: A new subscription has been successfully created + value: + protocol: HTTP + protocolSettings: + method: POST + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: '2023-01-17T13:18:23.682Z' + subscriptionMaxEvents: 5 + initialEvent: true + id: 550e8400-e29b-41d4-a716-446655440000 + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + ACTIVE_SUBSCRIPTION: + description: Details of an active subscription + value: + id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + description: Details of an active subscription with device details for disambiguation + value: + id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] +``` diff --git a/marked/DeviceDataVolume/code/API_definitions/device-data-volume/raw.md b/marked/DeviceDataVolume/code/API_definitions/device-data-volume/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..98ab8a990b4a55d321dca9d2b0d4bee591c9fd53 --- /dev/null +++ b/marked/DeviceDataVolume/code/API_definitions/device-data-volume/raw.md @@ -0,0 +1,554 @@ +# device-data-volume + +```yaml +openapi: 3.0.3 +info: + title: Device Data Volume + description: | + This API offers detailed insights into the customer's data usage status, including available data volume and their current position within the volume allocation. + + # Introduction + + API consumers are able to retrieve data usage information for a dedicated SIM card, offering estimated remaining data volume categories like <200MiB, <1GiB, <5GiB, and >=5GiB. It also allows subscription to changes in data volume status. + + Additionally, a check operation is provided to determine if the remaining data volume exceeds a user-specified threshold. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes two endpoints/operations: + + - The endpoint `POST /retrieve` allows customers to retrieve the remaining device data volume. + - The endpoint `POST /check` allows customers to check if the remaining data volume is above a certain threshold. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceDataVolume + +servers: + - url: "{apiRoot}/device-data-volume/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Device Data Volume + description: Operations related to remaining device data volume of a user device + +paths: + /retrieve: + post: + tags: + - Device Data Volume + summary: "Execute device data volume retrieval for a user device" + description: Retrieve the estimated remaining data volume for a device. + operationId: retrieveDataVolume + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-data-volume:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveDataVolumeRequest" + required: true + responses: + "200": + description: Contains information about the remaining device data volume. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveDataVolumeResponse" + examples: + Successful Response: + $ref: "#/components/examples/SuccessfulRetrieveResponse" + Successful Response With Device Disambiguation: + $ref: "#/components/examples/SuccessfulRetrieveResponseWithDeviceDisambiguation" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + + /check: + post: + tags: + - Device Data Volume + summary: "Check if the remaining data volume is above a certain threshold" + description: Check if the remaining data volume for a device is above a given threshold. + operationId: checkDataVolume + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-data-volume:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDataVolumeRequest" + required: true + responses: + "200": + description: Boolean response indicating if the remaining data volume exceeds the provided threshold + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDataVolumeResponse" + examples: + Successful Response: + $ref: "#/components/examples/SuccessfulCheckResponse" + Successful Response With Device Disambiguation: + $ref: "#/components/examples/SuccessfulCheckResponseWithDeviceDisambiguation" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CheckDataVolumeRequest: + description: | + The request to check, if the current remaining data volume is above the requested threshold. + Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + volumeToCheck: + type: object + description: Volume threshold to check against + properties: + value: + description: Quantity of volume to check + type: integer + example: 500 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/VolumeUnitEnum" + required: + - value + - unit + required: + - volumeToCheck + + VolumeUnitEnum: + description: Enumeration of volume units, where "MiB" is 2^20 bytes and "GiB" is 2^30 bytes. + type: string + enum: + - MiB + - GiB + + CheckDataVolumeResponse: + description: Represents the response, if the data volume exceeds a given threshold. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + thresholdExceeded: + type: boolean + description: Indicates whether the remaining data volume exceeds the given threshold + required: + - thresholdExceeded + + RetrieveDataVolumeRequest: + description: | + The request to retrieve the current remaining data volume for the requested device. + Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveDataVolumeResponse: + description: Represents the remaining data volume of the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + dataVolumeCategory: + $ref: "#/components/schemas/DataVolumeCategory" + required: + - dataVolumeCategory + + DataVolumeCategory: + description: Estimated remaining data volume category, where "MiB" is 2^20 bytes and "GiB" is 2^30 bytes. + type: string + enum: + - "<200MiB" + - "<1GiB" + - "<5GiB" + - ">=5GiB" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + summary: Missing identifier + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + summary: Unnecessary identifier + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + + examples: + SuccessfulRetrieveResponse: + description: Successfully retrieve the device data volume category + value: + dataVolumeCategory: "<200MiB" + SuccessfulRetrieveResponseWithDeviceDisambiguation: + description: Successfully retrieve the device data volume category but device disambiguation is required + value: + device: + phoneNumber: "+123456789" + dataVolumeCategory: "<200MiB" + SuccessfulCheckResponse: + description: Successfully check the device data volume category + value: + thresholdExceeded: false + SuccessfulCheckResponseWithDeviceDisambiguation: + description: Successfully check the device data volume category but device disambiguation is required + value: + device: + phoneNumber: "+123456789" + thresholdExceeded: true +``` diff --git a/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist/raw.md b/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d6b86ea02f4502780542eb506b24a6673c046069 --- /dev/null +++ b/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for device-data-volume v0.1.0 in r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-----------------:|:-----------------:|:------:|:---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-data-volume.yaml](/code/API_definitions/device-data-volume.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [checkDataVolume.feature](/code/Test_definitions/device-data-volume-checkDataVolume.feature)
          [retrieveDataVolume.feature](/code/Test_definitions/device-data-volume-retrieveDataVolume.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [checkDataVolume.feature](/code/Test_definitions/device-data-volume-checkDataVolume.feature)
          [retrieveDataVolume.feature](/code/Test_definitions/device-data-volume-retrieveDataVolume.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/wYFmBQ) | diff --git a/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..34c22c9223935499b8d747ab576b96f884fd8c27 --- /dev/null +++ b/marked/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for device-data-volume-subscriptions v0.1.0 in r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
          public | stable
          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-----------------:|:-----------------:|:------:|:----------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-data-volume-subscriptions.yaml](/code/API_definitions/device-data-volume-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [subscriptions.feature](/code/Test_definitions/device-data-volume-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [subscriptions.feature](/code/Test_definitions/device-data-volume-subscriptions.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/PIPFBQ) | diff --git a/marked/DeviceDataVolume/documentation/SupportingDocuments/README/raw.md b/marked/DeviceDataVolume/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceDataVolume/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceIdentifier/README/raw.md b/marked/DeviceIdentifier/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8685c7eea9db16e1e69892d5de1efe64e83f5055 --- /dev/null +++ b/marked/DeviceIdentifier/README/raw.md @@ -0,0 +1,52 @@ + + + + + + + + + +# DeviceIdentifier + +Sandbox API Repository to describe, develop, document, and test the DeviceIdentifier Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/czLe) + +## Scope + +* Service API “DeviceIdentifier” (see [APIBacklog](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API consumer with the ability to: + * Retrieve the current identity (IMEI) of the mobile device being used by a given mobile subscriber + * Retrieve the type (manufacturer and model) of the mobile device being used by a given mobile subscriber +* Describe, develop, document, and test the API +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/DeviceIdentifier/releases/tag/r2.2) (Fall25), with the following API versions: + * **device-identifier v0.3.0** + [[YAML]](https://github.com/camaraproject/DeviceIdentifier/blob/r2.2/code/API_definitions/device-identifier.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/r2.2/code/API_definitions/device-identifier.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/r2.2/code/API_definitions/device-identifier.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceIdentifier/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceIdentifier/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceIdentifier/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: First Friday of each month at 15:00 UTC via Linux Foundation Zoom service + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96981252767?password=fc957607-cc06-450f-b80a-229bb6a88c39) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564298/DeviceIdentifier+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list [https://lists.camaraproject.org/g/sp-dvi](https://lists.camaraproject.org/g/sp-dvi) . + * A message to the community of this Sub Project can be sent using [sp-dvi@lists.camaraproject.org](mailto:sp-dvi@lists.camaraproject.org). diff --git a/marked/DeviceIdentifier/code/API_definitions/device-identifier/raw.md b/marked/DeviceIdentifier/code/API_definitions/device-identifier/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..56d04493ddd2c94faac9f443c46a10a32328cc6c --- /dev/null +++ b/marked/DeviceIdentifier/code/API_definitions/device-identifier/raw.md @@ -0,0 +1,869 @@ +# device-identifier + +```yaml +openapi: 3.0.3 +info: + title: Device Identifier + version: wip + description: | + # Summary + + The Mobile Device Identifier API returns details of the physical mobile device currently being used by a specified mobile subscriber. The following information can be returned: + - A unique network identifier for the specific device itself (IMEI SV and IMEI) + - A pseudonymised network identifier for the specific device itself (Pairwise Pseudonymous Identifier) + - A network identifier for the device make and model (IMEI Type Allocation Code) + - Device manufacturer name and model + + This information can be useful in a number of scenarios, such as the following: + - For insurance purposes, to automatically identify a device that a customer wishes to insure + - For security / fraud reasons, to establish that a customer is not using a device they claim to have broken or lost + - For service delivery reasons, to optimise content for a particular device or OS type + + # Introduction + + Mobile devices are allocated a unique identifier by the manufacturer, known as the International Mobile Equipment Identity, or IMEI. The current software version (SV) of the device can be appended to this, in which case the identifier is known as the IMEI SV. This identifier is signalled to the mobile network when the device connects, both to confirm that the device is not blocked, and also allow device dependent network configurations to be implemented. + + The IMEI is a 15 digit integer, and the IMEI SV is a 16 digit integer: + - The first 8 digits are known as the Type Allocation Code (TAC), and identify the manufacturer and model of the device + - The following 6 digits are the serial number of the device for that TAC + - For IMEI, the remaining digit is a check digit + - For IMEI SV, the remaining two digits are the software version + + TACs are issued and managed by the GSMA, and can be queried using the [GSMA IMEI database](https://www.gsma.com/aboutus/workinggroups/terminal-steering-group/imei-database). + + The mobile network associates this device identifier with the mobile subscription currently using the device. The mobile subscription is defined by the Subscriber Identity Module (SIM) currently active in the mobile device. This may be a removable SIM or an eSIM. In either case, it is possible for the association between the device identifier and subscription to change - for example, when a physical SIM is transferred to another mobile device. + + ![Device Identifier API Overview](https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/main/documentation/API_documentation/resources/Device_Identifier_Overview.png) + + The Device Identifier API allows the API consumer to obtain the IMEI and associated parameters for a specified mobile subscription identifier or equivalent. The mobile subscription can be identified using one or more of the following subscription identifiers: + - the subscription phone number (also known as MSISDN) + - the subscription network access identifier, which is a domain specific identifier typically allocated to devices that do not require voice / SMS connectivity + - the current IP address and port alloacted to the device, which must be an IPv6 or public IPv4 address + + The API can be called by an API consumer to establish an identifier for the physical device currently being used by the mobile subscription. The information returned will depend upon the consent that the end user (i.e. mobile subscription owner) has given for that information to be provided to the API consumer. For example, if the end user has not consented to any information about their device being given, then the API consumer will receive an error in response to their request. Otherwise, the information that the end user has consented to being given will be returned. + + # Relevant terms and definitions + + ### Device Identifier API service endpoint + The URL pointing to the RESTful resource of the Device Identifier API. + + ### Identifier for the mobile subscription + At least one identifier for the mobile subscription from the following four options: + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + ### Identifier for the physical mobile device + The IMEI or IMEISV of the physical mobile device + + ### Pairwise Pseudonymous Identifier + An identifier that has been pseudonymised such that the resulting pseudonymous identifier is unique to but persistent for a given API consumer + + # API functionality + + The API defines three service endpoints: + + - `POST /retrieve-identifier` to get details about the specific device being used by a given mobile subscriber, including IMEI / IMEISV and the type of device + - `POST /retrieve-type` to get details only about the type (i.e. manufacturer and model) of device being used by a given mobile subscriber + - `POST /retrieve-ppid` to get a pseudonymised identifier for the specific device being used by a given mobile subscriber + + To call any of these endpoints, the API consumer must first obtain a valid access token from the token endpoint, which is then passed as an Authorization header. When a 2-legged access token is used, the API consumer must also pass at least one of the available mobile subscription identifiers in the body of the request. + + If the request is valid, the API response is a JSON object containing the data that the end user has consented to sharing with the API consumer. + - When calling endpoint `retrieve-identifier`, the response will always contain `imei` + - When calling endpoint `retrieve-type`, the response will always contain `tac` + - When calling endpoint `retrieve-ppid`, the response will always contain `ppid` + - Responses will also always contain a `lastChecked` field, indicating when the information provided was last confirmed to be correct + - Other response parameters are implementation dependent, and thus optional + + An example of a JSON response object is as follows: + ``` + { + "lastChecked": "2024-02-20T10:41:38.657Z", + "imeisv": "49015420323751800", + "imei": "4901542032375181", + "tac": "49015420", + "model": "3110", + "manufacturer": "Nokia" + } + ``` + + ## Error handling + + Errors may be returned for the following reasons. Note that this list is not exhaustive. + + `401 UNAUTHENTICATED`: + - The access token is not a valid access token for the API provider + - The access token was valid but has now expired + + `400 INVALID_ARGUMENT`: + - The API request is not compliant with this OAS definition + + `400 OUT_OF_RANGE`: + - A parameter value in the API request is outwith the range documented in this OAS definition for that parameter + + `404 IDENTIFIER_NOT_FOUND`: + - The device identified by the `device` object in the request is not managed by the API provider + + `403 PERMISSION_DENIED`: + - The access token does not have the required scope for the endpoint being called + - The end user has not consented to the API consumer getting access to the device identifier information (2-legged access token only) + + `422 SERVICE_NOT_APPLICABLE`: + - A device identifier cannot be provided for the identified device. For example, the phone number might identify a landline. + + `422 UNSUPPORTED_IDENTIFIER`: + - A parameter provided in the `device` object is not supported by this implementation (e.g. `networkAccessIdentifier`) + + `422 MISSING_IDENTIFIER`: + `422 UNNECESSARY_IDENTIFIER`: + - See the section "Identifying the device from the access token" below + + `429 QUOTA_EXCEEDED`: + - The API consumer has used up the quota of API requests that they were allocated for this API + + `429 TOO_MANY_REQUESTS`: + - The rate at which the API consumer is sending requests has exceeded that allowed by the API provider. Try again later. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In scenarios where a main phone number is shared between multiple devices, each of which has its own individual "secondary" phone number (e.g. connectivity plans that let you share your airtime and data allowances with a smartwatch or eSIM-enabled tablet), the phone number passed by the API consumer will be treated as the secondary phone number, and hence the identifier returned will be that of the single device associated with that phone number (e.g. smartphone, smartwatch, or eSIM-enabled tablet). + + In such scenarios, the "primary" device is usually allocated the same main and secondary phone numbers, and hence providing the main phone number to the API will return the identity of the primary device (usually the smartphone) and not any associated devices. + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceIdentifier + +servers: + - url: "{apiRoot}/device-identifier/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Get Device Identifiers + description: Retrieve details about the device being used by a mobile subscriber + +paths: + "/retrieve-identifier": + post: + summary: Get details about the specific device being used by a given mobile subscriber + description: Get details about the specific device being used by a given mobile subscriber + operationId: retrieveIdentifier + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-identifier + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrieveIdentifier' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + + "/retrieve-type": + post: + summary: Get details about the type of device being used by a given mobile subscriber + description: Get details about the type of device being used by a given mobile subscriber + operationId: retrieveType + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-type + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrieveType' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + + "/retrieve-ppid": + post: + summary: Get a pseudonymous identifier for device being used by a given mobile subscriber + description: Get a pseudonymous identifier for device being used by a given mobile subscriber + operationId: retrievePPID + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-ppid + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to identify the mobile subscription when a 2-legged access token is being used + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrievePPID' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + 200RetrieveIdentifier: + description: An device identifier has been found for the specified subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - imei + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DeviceIdentifier" + - $ref: "#/components/schemas/DeviceType" + examples: + Successful Identifier Retrieval: + description: Device identifier has been successfully retrieved when the device subscription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imeisv: "49015420323751800" + imei: "4901542032375181" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + Successful Identifier Retrieval With Device Disambiguation: + description: Device identifier has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + imeisv: "49015420323751800" + imei: "4901542032375181" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + + 200RetrieveType: + description: A device identifier has been found for the specified subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - tac + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DeviceType" + examples: + Successful Type Retrieval: + description: Device type has been successfully retrieved when the device subcsription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + Successful Type Retrieval With Device Disambiguation: + description: Device type has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + + 200RetrievePPID: + description: A pseudonymous device identifier has been found for the specified mobile subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - ppid + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DevicePPID" + examples: + Successful PPID Retrieval: + description: Device PPID has been successfully retrieved when the device subcsription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + ppid: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + Successful PPID Retrieval With Device Disambiguation: + description: Device PPID has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + ppid: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + + 400BadRequest: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: OUT_OF_RANGE + message: "Invalid value: ipv4Address.publicPort" + + 401Unauthorized: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated Request: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + 403Forbidden: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permision Denied: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + 404NotFound: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + Device Cannot Be Found: + description: The provided identifier cannot be matched to a device known to the API provider + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The provided identifier cannot be matched to a device. + + 422UnprocessableContent: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Service Not Applicable For Device: + description: The service is not applicable for the identified device + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the identified device. + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + + 429TooManyRequests: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + Too Many Requests: + description: Access to the API has been temporarily blocked due to quota or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached + Quota Exceeded: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota + + schemas: + CommonResponseBody: + description: | + Common parameters to be included in all responses + properties: + device: + description: The device subscription identifier that was used to identify the device whose identifier is being returned. If this property is not present, then the device subscription identifier specified in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + lastChecked: + description: | + Date and time that the information was last confirmed by the mobile operator to be correct. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + DeviceIdentifier: + description: | + The individual physical mobile device identifier, as expressed by the IMEI and IMEISV + type: object + properties: + imeisv: + type: string + description: IMEISV of the device + example: "49015420323751800" + imei: + type: string + description: IMEI of the device + example: "4901542032375181" + + DeviceType: + description: | + The physical device type, as expressed by Type Approval Code, manufacturer name and model name + type: object + properties: + tac: + type: string + description: IMEI TAC of the device + example: "49015420" + model: + type: string + description: Model of the device + example: "3110" + manufacturer: + type: string + description: Manufacturer of the device + example: "Nokia" + + DevicePPID: + description: | + The individual physical mobile device identifier, expressed as a PPID (Pairwise Pseudonymous Identifier) + type: object + properties: + ppid: + type: string + description: A PPID for the identified physical device + example: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE 1: The MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + NOTE 2: For the current Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "84.125.93.10", + "publicPort": 59765 + } + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + RequestBody: + description: Common request body to allow optional Device object to be passed + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + {} + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@example.com" +``` diff --git a/marked/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story/raw.md b/marked/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f338610321009ab95b21476000246949a30d0448 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story/raw.md @@ -0,0 +1,44 @@ +# Device Identifier API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want my application server to be able to request the identity of the mobile device (represented by the IMEI) currently being used by a given mobile network subscriber (identified by MSISDN, IP address or, when supported by network operators, a Network Access Identifier). Optionally, I'd like to know the make and model of that device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
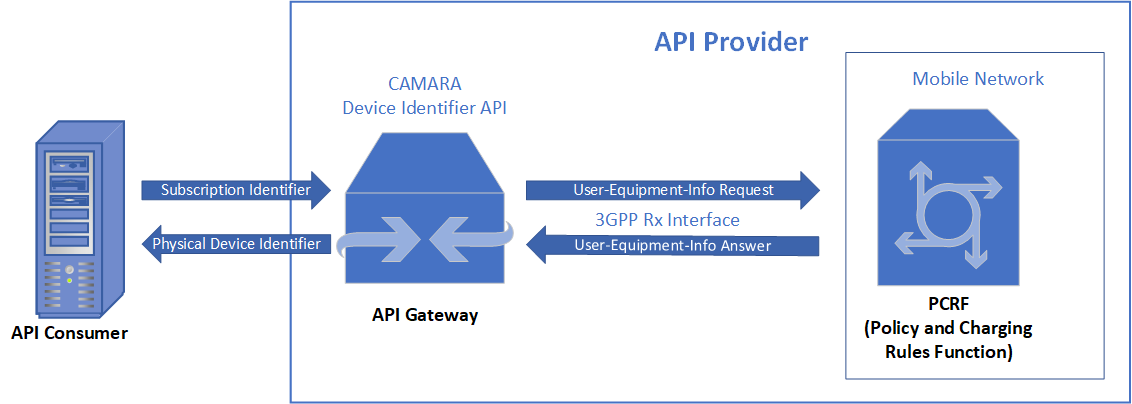
          **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
          **Scope:** *Order To Activate (OTA)* \- Retrieve device identifier details | +| ***Pre-Conditions*** |The preconditions are listed below:
          1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
          2. The Customer:BusinessManager has successfully subscribed to the Device Identifier product from the product catalog.
          3. The Customer:Administrator has onboarded the Customer:User to the platform.
          4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
          5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User's application server makes a POST request to the Device Identifier API containing the end user's subscription information in the request body in order to retrieve the device identifier plus any optional device information.
            **Ends when:** The Device Identifier API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Identifier API
            - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
            - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
            - **Forbidden**: End user has not consented to device identifier information being provided to the Customer:User| + +# EUDI Wallet Device-Binding User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer working for an EUDI Wallet provider, I want to bind the user's wallet to their device. For that purpose I want to retrieve the device identifier of the user's device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
            **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
            **Scope:** *Order To Activate (OTA)* \- Retrieve device identifier details | +| ***Pre-Conditions*** |The preconditions are listed below:
            1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
            2. The Customer:BusinessManager has successfully subscribed to the Device Identifier product from the product catalog.
            3. The Customer:Administrator has onboarded the Customer:User to the platform.
            4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
            5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User has installed the EUDI Wallet and the wallet runs for the first time. The EUDI Wallet retrieves an access-token using OIDC authentication code flow and creates a POST request to the DeviceIdentifier API to retrieve the device identifer.
              **Ends when:** The Device Identifier API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Identifier API
              - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
              - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
              - **Forbidden**: End user has not consented to device identifier information being provided to the Customer:User| + +# Device Type API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want my application server to be able to request details about the type of the mobile device (represented by the Type Approval Code - TAC) currently being used by a given mobile network subscriber (identified by MSISDN, IP address or, when supported by network operators, a Network Access Identifier). Optionally, I'd like to know the make and model of that device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
              **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
              **Scope:** *Order To Activate (OTA)* \- Retrieve device type details | +| ***Pre-Conditions*** |The preconditions are listed below:
              1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
              2. The Customer:BusinessManager has successfully subscribed to the Device Type product from the product catalog.
              3. The Customer:Administrator has onboarded the Customer:User to the platform.
              4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
              5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User's application server makes a POST request to the Device Type API containing the end user's subscription information in the request body in order to retrieve the device TAC plus any optional device information.
                **Ends when:** The Device Type API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Type API
                - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                - **Forbidden**: End user has not consented to device TAC information being provided to the Customer:User| + +# Mobile Device Insurance User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer working for an insurance company that insures mobile devices, I want to retrieve the device identifier and the model and make of the user's device. The retrieved information is used in creating the contract between the insurance company and the user, and also when the user reports the device to be e.g. damaged or stolen. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
                **Scope:** *Order To Activate (OTA)* \- Retrieve device type details | +| ***Pre-Conditions*** |The preconditions are listed below:
                1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                2. The Customer:BusinessManager has successfully subscribed to the Device Type product from the product catalog.
                3. The Customer:Administrator has onboarded the Customer:User to the platform.
                4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
                5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:Applicatoin requests an access token using OIDC authorization code flow and then uses the DeviceIdentifier API to retrieve device identifier and model and make of the user's devive.
                  **Ends when:** The Device Type API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Type API
                  - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                  - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                  - **Forbidden**: End user has not consented to device TAC information being provided to the Customer:User| + diff --git a/marked/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist/raw.md b/marked/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..400912877f851f19c5cb2bb1c07673e0f0ecfe98 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for device-identifier v0.3.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                  public | stable
                  public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-identifier.yaml](/code/API_definitions/device-identifier.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [Device Identifier User Story.md](/documentation/API_documentation/Device%20Identifier%20User%20Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-identifier-retrieveIdentifier.feature](/code/Test_definitions/device-identifier-retrieveIdentifier.feature)
                  [device-identifier-retrieveType.feature](/code/Test_definitions/device-identifier-retrieveType.feature)
                  [device-identifier-retrievePPID.feature](/code/Test_definitions/device-identifier-retrievePPID.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/goHWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..781a9d1a2498328d697ad2e5695abdf9cbb39516 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09/raw.md @@ -0,0 +1,12 @@ +# Meeting Minutes: Device Identifier WG +## Date: 9th December 2022 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- None +## Issues +- None +## Discussions +- None +## AOB +- No meeting on 23rd December 2022. Next meeting will be 6th January 2023. diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a5c64e6ceed9f03925f4270b747724e5519de6d6 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06/raw.md @@ -0,0 +1,21 @@ +# Meeting Minutes: Device Identifier WG +## Date: 6th January 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- None +## Issues +- None +## Discussions +### API Definition +- Eric presented an overview of the current [API definition](https://github.com/camaraproject/DeviceIdentifier/blob/main/code/API_definitions/CAMARA%20Device%20Identifier%20API.yaml). The following points were clarified: + - A `GET` call is used by this API as it is directly retrieving information from the network and not creating any sort of resource or subscription + - The agreed set of parameters used to identify a UE for all APIs (i.e. External Identifier, MSISDN and/or IP address) are used here, but passed as headers as these parameters are clearly sensitive and there is no request body to put them in. These parameters will evolve when discussions within the Commonalities WG on UE identification and user consent are concluded. + - The API can return up to 5 parameters related to the device being used by the identified UE (imei, imeisv, tac, manufacturer and model). None of these parameters is mandatory as it is an open question as to how user consent will affect the parameters that can be returned. It may be that the end user can grant or withhold consent individually for each parameter (even though some parameters can be derived from others). This issue will be revisited once the user consent process is finalised. + - Should response headers be standardised across all APIs? Or should there be a "default" set, with only additional headers listed? This is related to the API design guidelines. **Eric to open an issue in the Commonalities WG to discuss.** +### API Documentation +- API documentation will be generated once the above issue on response parameters is resolved. +## AOB +- Next meeting Friday 20th January @ 15:00 GMT diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a82c6cbd132b3e18d8bf142929566fbc294d9fde --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20/raw.md @@ -0,0 +1,18 @@ +# Meeting Minutes: Device Identifier WG +## Date: 20th January 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- [PR #7](https://github.com/camaraproject/DeviceIdentifier/pull/7) + This is an update to the API specification to remove non-essential headers (currently being discussed in [Commonalities Issue #124](https://github.com/camaraproject/WorkingGroups/issues/124)) and extend error responses to multiple examples using `examples` rather than a single `example`. No comments raised, so will merge this PR next week. +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4): Update commonalities glossary with subproject relevant terms** + - Request from Shilpa to add WG specific terminology to the glossary. Primarily the responsibility of the WG lead, but anybody can contribute. +## Discussions +### WG Code Owners +- Current code owners are both from Vodafone. It would be useful to have additional code owners from other companies. + - **Currently neither Ludovic nor Rafal can commit to this** +## AOB +- Next meeting Friday 3rd February @ 15:00 GMT diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..15b88ce71dff181db7652b4b59e7c7dd2ca3c038 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03/raw.md @@ -0,0 +1,16 @@ +# Meeting Minutes: Device Identifier WG +## Date: 3rd February 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- None outstanding +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4): Update commonalities glossary with subproject relevant terms** + - Still outstanding. +## Discussions +### API Evolution +- V0.0.1 of the API has now been merged into the main branch. Further evolution of the API will depend on ongoing discussions within the Commonalities WG, particularly around the design guidelines and common API definitions. No further updates will be proposed until these issues are finalised. +## AOB +- Next meeting Friday 17th February @ 15:00 GMT diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5c4f6c5bb0e35c3f88482b6c72a886d6fd047eb8 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17/raw.md @@ -0,0 +1,13 @@ +# Meeting Minutes: Device Identifier WG +## Date: 17th February 2023 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- None outstanding +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4) Update commonalities glossary with subproject relevant terms** + - Glossary terms submitted. Issue now closed. +## Discussions +- None +## AOB +- Next meeting Friday 3rd March @ 15:00 GMT diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ae62fadf6ed48bb1e3a377e21fd702463317fdb2 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17/raw.md @@ -0,0 +1,19 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 17th March 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Chris Howell / Vonage +- Shahram Mohajeri / AT&T +- Jussi Makela / CodeB +- Stefan Engelbert / CodeB +## Pull Requests +- None outstanding +## Issues +- None outstanding +## Discussions +- **API Overview** + - Eric gave a brief overview of the API for new attendees +## AOB +- Next meeting Friday 31st March @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..df7120c4e468189669e91fce5dd73e3495a4c440 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31/raw.md @@ -0,0 +1,17 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 31st March 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- **[PR #13](https://github.com/camaraproject/DeviceIdentifier/pull/13) Update CAMARA Device Identifier API.yaml** + - Specification changes to be compliant with current design and documentation guidelines in Commonalities WG + - Will be merged by CoB 6th April if no comments +## Issues +- None Outstanding +## Discussions +- **Meeting Cadence** + - Agreed to make meetings monthly given low meeting attendance and dependencies on other CAMARA working groups and sub-projects +## AOB +- Next meeting Friday 28th April @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..28178b757b10e76d0e06989c7dd8c37c3b6bf60b --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28/raw.md @@ -0,0 +1,26 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 28th April 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Chris Howell / Vonage +- Shahram Mohajeri / AT&T +- Jussi Makela / CodeB +- Nevin Aquinas / Vodafone +## Pull Requests +- None open +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Proposal is to return an additional device identifer if the primary device is associated with a secondary device (such as a smartwatch). The end user will know that they have such a device, but may not know any idenifiers for the SIM being used in that device. + - Ludovic asked how the mobile network would be aware of this association. Eric to update the issue with more information. +- **[Issue #20](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Documentation needs to be updated given decision in Commonalities to embed documentation in API OAS definition using markdown and HTML + - Eric to open PR with proposed documentation before next meeting +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Some property names used in the API definition do not match those in the Commonalities glossary. Additionally, some terms used in the API are not in the glossary. + - Eric to update names along with adding documentation, and also to submit PR to update glossary as appropriate. +## Discussions +- None +## AOB +- Next meeting Friday 26th May @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..265aa373327aba751ddefe23bae700c74192a09f --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26/raw.md @@ -0,0 +1,20 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 26th May 2023 +## Attendees +- Eric Murray / Vodafone +- Toshiyasu Wakayama / KDDI +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Adds documentation to API description + - Will be approved and merged before next meeting if no comments before +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Additional information provided on how secondary devices associated with the primary MSISDN are identified +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - No update +- **[Issue #16](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Will be closed by [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) +## Discussions +- None open +## AOB +- Next meeting Friday 23rd June @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b8c5cc8d754683e7283af8a279cf41753095b9db --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23/raw.md @@ -0,0 +1,26 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 23rd June 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Tim Kittel / Rohde & Schwarz +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Adds documentation to API description + - Request to add indication of supporting network element as SCEF / NEF does not provide IMEI + - In this case, IMEI can be obtained from PCRF over Rx interface. Suggested implementation to be added to documentation. + - Will be approved and merged before next meeting if no other comments before + - Following update will be to replace GET with POST as this method is now approved in CAMARA Design Guidelines +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Additional information provided on how secondary devices associated with the primary MSISDN are identified + - Issue discussed, but no update +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - No update, waiting for approval of [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24). +- **[Issue #16](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Will be closed by [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) +## Discussions +- None open +## AOB +- Next meeting Friday 21st July @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7f144ceb4abb50bf79b66bd01c5f23e34d20e638 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21/raw.md @@ -0,0 +1,25 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 21st July 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Approved and merged +- **[PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27) Update CAMARA Device Identifier API.yaml** + - Changes method of sensitive input parameters from GET headers to POST body following update to CAMARA API design guidelines + - This change would bring Device Identifier API into line with other APIs that use this method of passing sensitive parameters (e.g. Device Status, Device Location) + - PR to remain open for now in case of any discussion. Can be approved at next meeting if no objections. +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - No update, but no appetite to progress this + - Will be closed at next meeting if no other CAMARA participants express a requirement for this functionality +- **[Issue #20](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Now closed +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Waiting for approval of [PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27). +## Discussions +- None open +## AOB +- Skipping August meeting due to holidays, so next meeting will be Friday 15th September @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..da88fd6aa19e964713be45159c178bdbe49a12d8 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15/raw.md @@ -0,0 +1,24 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 15th September 2023 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- **[PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27) Update CAMARA Device Identifier API.yaml** + - Changes method of sensitive input parameters from GET headers to POST body following update to CAMARA API design guidelines + - This change would bring Device Identifier API into line with other APIs that use this method of passing sensitive parameters (e.g. Device Status, Device Location) + - **PR approved as no comments. Can be now merged.** +- **[PR #29](https://github.com/camaraproject/DeviceIdentifier/pull/29) Update README.md** + - Add links to Swagger Editor and ReDoc formatted versions of current WIP specification + - **PR approved as no comments. Can now be merged.** +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Issue to be closed as no interest +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Can be progressed with conclusion to be agreed at next meeting +- **[Issue #30](https://github.com/camaraproject/DeviceIdentifier/issues/30) Security Schemes and Scopes for Device Identifier API** + - New issue containing proposal for security schemes and scopes to be adopted by the Device Identifier API + - Will leave open for comments until next meeting +## Discussions +- None open +## AOB +- Next meeting will be Friday 13th October @ 15:00 BST diff --git a/marked/DeviceIdentifier/documentation/MeetingMinutes/README/raw.md b/marked/DeviceIdentifier/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d529e8a286c68e2c29877c234a3e35b838f61bc1 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +Later meeting minutes can now be found in the CAMARA wiki [here](https://wiki.camaraproject.org/display/CAM/Device+Identifier+Meeting+Minutes) diff --git a/marked/DeviceIdentifier/documentation/SupportingDocuments/README/raw.md b/marked/DeviceIdentifier/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..220f01caa5a015a6cfd54e60ac74769669ec4546 --- /dev/null +++ b/marked/DeviceIdentifier/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/marked/DeviceLocation/README/raw.md b/marked/DeviceLocation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..314ab38294720ce673f4c7a826e08e73e8e6a1f5 --- /dev/null +++ b/marked/DeviceLocation/README/raw.md @@ -0,0 +1,63 @@ + + + + + + + + + +# DeviceLocation + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceLocation Service API(s) within the Sub Project [Device Location](https://lf-camaraproject.atlassian.net/wiki/x/wgApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/GDLe) + +## Scope +* Service APIs for “Device Location” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * verify the location of a device (location-verification). + * retrieve the location of a device (location-retrieval). + * subscribe and receive notifications about a device entering or leaving certain location (geofencing-subscriptions). + * NOTE: The scope of these APIs is limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/DeviceLocation/releases/tag/r3.2) (Fall25), with the following API versions: + * **geofencing-subscriptions v0.5.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/geofencing-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/geofencing-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/geofencing-subscriptions.yaml) + * **location-retrieval v0.5.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/location-retrieval.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-retrieval.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-retrieval.yaml) + * **location-verification v3.0.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/location-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceLocation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceLocation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceLocation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + - Schedule: bi-weekly (odd weeks), Tuesday, 8:00 AM UTC (9:00 CET/10:00 CEST) + - Meeting link: [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91878854906?password=7e620a89-fcb5-4d2d-927a-17e3a0d1d28e) +* Mailing list: + - To subscribe / unsubscribe to the mailing list of this Sub Project, please visit . + - A message to the community of this Sub Project can be sent using . +* Slack channel: [camara-project.slack.com](https://join.slack.com/t/camara-project/shared_invite/zt-26gy3e64n-o7Riy3MoXmzdaDEL3wlngg) #sp-device-location diff --git a/marked/DeviceLocation/code/API_definitions/geofencing-subscriptions/raw.md b/marked/DeviceLocation/code/API_definitions/geofencing-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..58a7e3853c07c75edb16a9d9ce1ef5332d2d967d --- /dev/null +++ b/marked/DeviceLocation/code/API_definitions/geofencing-subscriptions/raw.md @@ -0,0 +1,1791 @@ +# geofencing-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Geofencing Subscriptions + description: | + API to create, retrieve and delete event subscriptions to realize geofencing for a user device. + + # Introduction + + With this API, API consumers can create subscriptions for their devices to receive notifications when a device enters or exits a specified area. + + * If the provided area is out of the operator's coverage or it is not supported for any reason, an error `422 GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED` will be returned. + * Legal restrictions regarding privacy, or other regulatory or implementation issues, may force the operator to set restrictions to the provided area, such as setting a minimum value to the accepted radius. In these cases, an error `422 GEOFENCING_SUBSCRIPTIONS.INVALID_AREA` will be returned and the error message will refer to the reason of the limitation. + + The area provided in the request is described by a circle determined by coordinates (latitude and longitude) and an accuracy defined by the radius. + + Upon successfully creating a subscription, the API will provide an Event Subscription ID, and it will indicate the subscription's expiration date. + + If the geofencing-state of a device changes, the event subscriber will be notified back to the provided Notification-Url given by the subscription-request. + + Device geofencing API could be useful in scenarios such as: + + - Tracking devices for Presetting of Home-Settings + - Tracking of logistics + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface which a device is planned to enter or exit. + + # API Functionality + + The API exposes following capabilities: + + ## Device Geofencing subscription + These endpoints allow to manage event subscription on geofencing device location event. + + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.geofencing-subscriptions.v0.area-entered`` - Event triggered when the device enters the given area + + - ``org.camaraproject.geofencing-subscriptions.v0.area-left`` - Event triggered when the device leaves the given area + + Note: Additionally, the following events could be send, which do not require a dedicated subscription: + - `org.camaraproject.geofencing-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.geofencing-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.geofencing-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used when: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + - the specified geofence-`area` cannot be covered or is too small to be managed + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding geofencing can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may behave: + + - rejecting the subscription with an error indicating that that phone number is not supported for this API, or + - generating events for a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - generating events for of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/DeviceLocation + +servers: + - url: "{apiRoot}/geofencing-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Geofencing subscriptions + description: Operations to manage event subscriptions on geofencing events for leaving and entering an area. +paths: + /subscriptions: + post: + tags: + - Geofencing subscriptions + summary: "Create a geofencing subscription for a device" + description: Create a subscription for a device to receive notifications when the device enters or exits a specified area. + operationId: createGeofencingSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - geofencing-subscriptions:org.camaraproject.geofencing-subscriptions.v0.area-entered:create + - geofencing-subscriptions:org.camaraproject.geofencing-subscriptions.v0.area-left:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + CIRCLE_AREA_ENTERED: + $ref: "#/components/examples/REQUEST_CIRCLE_AREA_ENTERED" + REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS: + $ref: "#/components/examples/REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: This endpoint is to be implemented by the API consumer. + The Geofencing server will call this endpoint whenever a Geofencing event occurs. + The `operationId` value will have to be replaced accordingly with WG API specific semantics. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + CIRCLE_AREA_ENTERED: + $ref: "#/components/examples/CIRCLE_AREA_ENTERED" + CIRCLE_AREA_LEFT: + $ref: "#/components/examples/CIRCLE_AREA_LEFT" + SUBSCRIPTION_STARTED: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + SUBSCRIPTION_UPDATED: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + SUBSCRIPTION_ENDED: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + SUBSCRIPTION_UNPROCESSABLE: + $ref: "#/components/examples/SUBSCRIPTION_UNPROCESSABLE" + responses: + "204": + description: Successful notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - notificationsBearerAuth: [] + - {} + responses: + "201": + description: Created (Successful creation of subscription). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Geofencing subscriptions + summary: "Retrieve a list of geofencing event subscription" + description: Retrieve a list of geofencing event subscription(s). + operationId: retrieveGeofencingSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - geofencing-subscriptions:read + responses: + "200": + description: List of event subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Geofencing subscriptions + summary: "Operation to retrieve a subscription based on the provided ID" + description: Retrieve Geofencing subscription information for a given subscription ID. + operationId: retrieveGeofencingSubscription + security: + - openId: + - geofencing-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Geofencing subscriptions + summary: "Delete a Geofencing event subscription" + operationId: deleteGeofencingSubscription + description: Delete a given Geofencing subscription. + security: + - openId: + - geofencing-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Geofencing subscription deleted. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + description: OpenID Connect authentication. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation. + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ErrorInfo: + description: The error info object for possible error cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code. + code: + type: string + description: A human-readable code to describe the error. + message: + type: string + description: A human-readable description of what the event represents. + + SubscriptionRequest: + description: The request for creating an event-type event subscription. + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types which are eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/ConfigRequest" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now. + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + type: object + properties: + subscriptionExpireTime: + type: string + format: date-time + example: "2023-01-17T13:18:23.682Z" + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + Note on combined usage of `initialEvent` and `subscriptionMaxEvents`: + If an event is triggered following `initialEvent` set to `true`, this event will be counted towards `subscriptionMaxEvents`. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered. + + ConfigRequest: + allOf: + - $ref: "#/components/schemas/Config" + - description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + Specific event type attributes requested by the client must be defined in `subscriptionDetail`. + Note: If a request is performed for several event types, all subscribed events will use the same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetailRequest" + + ConfigResponse: + allOf: + - $ref: "#/components/schemas/Config" + - description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + Specific event type attributes granted by the implementation are included in `subscriptionDetail`. + Note: If a request is performed for several event types, all subscribed events will use the same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetailResponse" + + + SinkCredential: + type: object + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + properties: + credentialType: + type: string + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetailRequest: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + required: + - area + + SubscriptionDetailResponse: + description: The detail of the event subscription granted by the implementation. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + required: + - area + + SubscriptionEventType: + type: string + description: | + area-entered - Event triggered when the device enters the given area + + area-left - Event triggered when the device leaves the given area + enum: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + - org.camaraproject.geofencing-subscriptions.v0.area-left + + NotificationEventType: + type: string + description: | + area-entered - Event triggered when the device enters the given area + + area-left - Event triggered when the device leaves the given area + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends + enum: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + - org.camaraproject.geofencing-subscriptions.v0.area-left + - org.camaraproject.geofencing-subscriptions.v0.subscription-started + - org.camaraproject.geofencing-subscriptions.v0.subscription-updated + - org.camaraproject.geofencing-subscriptions.v0.subscription-ended + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/ConfigResponse" + id: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: "1119920371" + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: Response for an event-type subscription request managed asynchronously (Creation or Deletion). + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the API provider might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different API providers. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response or event. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks, it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask. + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number. + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Area: + type: object + description: The geofencing area where the monitor is active. This area is specified by API consumers in the subscription request. The same area definition is included in event notifications without any modifications. + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + enum: + - CIRCLE + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: | + Expected accuracy for the subscription event of device location, in meters from `center`. + Note: The area surface could be restricted locally depending on regulations. Implementations may enforce a larger minimum radius (e.g. 1000 meters). + minimum: 1 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map. + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location. + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component of location. + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + CloudEvent: + description: The notification callback. + required: + - id + - source + - specversion + - type + - time + - data + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/NotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version). + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type. + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.geofencing-subscriptions.v0.area-left: "#/components/schemas/EventAreaLeft" + org.camaraproject.geofencing-subscriptions.v0.area-entered: "#/components/schemas/EventAreaEntered" + org.camaraproject.geofencing-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.geofencing-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.geofencing-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventAreaLeft: + description: Event structure for event when the device leaves the area. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaLeft" + + EventAreaEntered: + description: Event structure for event when the device enters the area. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaEntered" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + - area + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - area + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: Event structure for event subscription ends. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + AreaLeft: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.area-left event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + AreaEntered: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.area-entered event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.subscription-ended event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_UNPROCESSABLE - Subscription cannot be processed due to some reason, e.g. because the specified area cannot be managed. Useful for asynchronous subscription creation. + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_UNPROCESSABLE + - SUBSCRIPTION_EXPIRED + - SUBSCRIPTION_DELETED + - ACCESS_TOKEN_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_PROTOCOL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_PROTOCOL: + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported. + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported. + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Schema validation failed + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + summary: The subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_TOKEN_MISMATCH: + value: + status: 403 + code: SUBSCRIPTION_MISMATCH + message: Inconsistent access token for requested events subscription. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: + Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED + - GEOFENCING_SUBSCRIPTIONS.INVALID_AREA + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GEOFENCING_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED + message: "Unable to cover the requested area" + GEOFENCING_422_INVALID_AREA: + summary: Invalid area + description: The requested area is too small to be supported by the system. + value: + status: 422 + code: GEOFENCING_SUBSCRIPTIONS.INVALID_AREA + message: "The requested area is too small" + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + REQUEST_CIRCLE_AREA_ENTERED: + description: A sample geofence for entering for a circle area. + value: + protocol: "HTTP" + sink: https://notificationSendServer12.supertelco.com + types: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + config: + subscriptionDetail: + device: + phoneNumber: "+12345678912" + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS: + description: A sample geofence for entering for a circle area. + value: + protocol: "HTTP" + sink: https://notificationSendServer12.supertelco.com + types: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + config: + subscriptionDetail: + device: + phoneNumber: "+12345678912" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + CIRCLE_AREA_ENTERED: + description: The cloud event when a geofence area was entered. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.area-entered + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + CIRCLE_AREA_LEFT: + description: The cloud event when a geofence area was left. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.area-left + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + + SUBSCRIPTION_STARTED: + description: The cloud event when a geofence subscription was started. + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: dv10-h556-rt89-1403 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a geofence subscription was updated. + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: dv10-h556-rt89-1403 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a geofence subscription ended. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + terminationReason: SUBSCRIPTION_EXPIRED + + SUBSCRIPTION_UNPROCESSABLE: + description: The cloud event when the subscription process was aborted. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + terminationReason: SUBSCRIPTION_UNPROCESSABLE + terminationDescription: The requested area cannot be covered by the network. +``` diff --git a/marked/DeviceLocation/code/API_definitions/location-retrieval/raw.md b/marked/DeviceLocation/code/API_definitions/location-retrieval/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8ece3c086b2671f42783c2c22c95df4746fae8e0 --- /dev/null +++ b/marked/DeviceLocation/code/API_definitions/location-retrieval/raw.md @@ -0,0 +1,687 @@ +# location-retrieval + +```yaml +openapi: 3.0.3 +info: + title: Device Location Retrieval + description: | + This API provides the ability to retrieve a device location. + + # Introduction + + With this API, API consumers can retrieve the area where a certain user device is localized. + The area provided in the response could be described: + - by a circle determined by coordinates (latitude and longitude) and a radius. + - by a simple polygon delimited by segments connecting consecutively an array of coordinates (points). The last point connects to the first point to delimit a closed shape bounded with straight sides. + + The retrieved shape depends on the network conditions at the device's location and any of the supported shapes could be received. + + The requester could optionally ask for + * a freshness of the localization information by providing a `maxAge` ("I want a location not older than 600 seconds"). + * an accuracy of the localization information by providing a `maxSurface` ("I want a location not larger than 1000000 square meters"). + + + The result accuracy depends on the network's ability and accuracy to locate the device. + + Additionally to location information, the answer will also provide indication about the location time. + + Location retrieval API could be useful in scenarios such as: + + - Fraud protection to ensure a given user is located in the region, country or location authorized for financial transactions + - Verify the GPS coordinates reported by the app on a device to ensure the GPS was not faked e.g. for content delivery with regional restrictions + - Contextual-based advertising, to trigger advertising after verifying the device is in the area of interest + + - Smart Mobility (Vehicle/bikes renting): obtain the location of a vehicle/bike to guarantee they are rented correctly + + **Note**: Location is in most jurisdictions considered to be sensitive data and thereby consent by device owner/user must be verified before providing it to the developer. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface where a device may be physically located. + + * **Max Age**: Maximum age of the location information which is accepted for the location retrieval (in seconds). + + * Absence of `maxAge` means that "any age" is acceptable for the client. In other words, this is like `maxAge`=infinite. The system will return `lastLocationTime` in the response. If the system is not able to provide location, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_LOCATE is sent back. + * `maxAge`=0 means that a fresh calculation is requested by the client. If the system is not able to provide the fresh location, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE is sent back. + + * **Last Location Time** : Last date and time when the device was localized. + + * **Max Surface**: Maximum surface in square meters which is accepted by the client for the location retrieval. + + * absence of `maxSurface` means that "any surface size" is acceptable for the client. + * API implementation could specify the minimum acceptable `maxSurface` in the documentation (for example a minimum of 10000 square meters are allowed). + * If the system is not able to provide an area with a surface acceptable with the client request, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE is sent back. + * Note: if both `maxAge` and `maxSurface` requirements fail, the system can either send back one or the other error code. + + # API Functionality + + The API exposes a single endpoint/operation: + + - `/retrieve` : Retrieve where the device is localized. + The operation returns: + * a localization defined either as a circle, with the center specified by the latitude and longitude, and a radius for answer accuracy, or as polygon defined by the array of points delimiting its boundary. + * a timestamp with the location information freshness. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may response with: + + - an error indicating that that phone number is not supported for this API, or + - the location of a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - a location value that combines the location of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/DeviceLocation +servers: + - url: '{apiRoot}/location-retrieval/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Location retrieval + description: Retrieve the location of a device +paths: + /retrieve: + post: + tags: + - Location retrieval + summary: 'Execute location retrieval for a user device' + description: Retrieve the area where a certain user device is localized. + operationId: retrieveLocation + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/RetrievalLocationRequest' + examples: + INPUT_PHONE_NUMBER_MAX_AGE: + summary: Phone number and maxAge + description: Retrieve location for a device identified by a phone number, providing a maxAge + value: + device: + phoneNumber: "+123456789" + maxAge: 120 + INPUT_PHONE_NUMBER_MAX_AGE_AND_SURFACE: + summary: Phone number, maxAge and maxSurface + description: Retrieve location for a device identified by a phone number, providing a maxAge and maxSurface + value: + device: + phoneNumber: "+123456789" + maxAge: 120 + maxSurface: 1000000 + INPUT_IP_ADDRESS_V4: + summary: IPv4 address without maxAge + description: Retrieve location for a device identified by an IPv4 address, without an indication for maxAge + value: + device: + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + INPUT_NO_DEVICE_AND_MAX_AGE: + summary: Device not provided, only maxAge + description: The device has to be deducted from token + value: + maxAge: 120 + INPUT_PHONE_NUMBER_IP_ADDRESS_V4: + summary: Both phone number and IPv4 address, without maxAge + description: Retrieve location for a device identified both by a phone number and an IPv4 address, without an indication for maxAge + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + responses: + '200': + description: Location retrieval result + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/Location' + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + LOCATION_CIRCLE_WITH_DEVICE: + $ref: "#/components/examples/LOCATION_CIRCLE_WITH_DEVICE" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/RetrieveLocationNotFound404' + '422': + $ref: '#/components/responses/RetrieveLocationUnprocessableEntity422' + security: + - openId: + - location-retrieval:read + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RetrievalLocationRequest: + description: Request to retrieve the location of a device. Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: '#/components/schemas/Device' + maxAge: + type: integer + minimum: 0 + description: Maximum age of the location information which is accepted for the location retrieval (in seconds). Absence of maxAge means "any age" and maxAge=0 means a fresh calculation. + maxSurface: + type: integer + minimum: 1 + description: Maximum surface in square meters which is accepted by the client for the location retrieval. Absence of maxSurface means "any surface size". + example: 1000000 + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Location: + type: object + description: Device location + required: + - lastLocationTime + - area + properties: + lastLocationTime: + $ref: "#/components/schemas/LastLocationTime" + area: + $ref: '#/components/schemas/Area' + device: + $ref: "#/components/schemas/DeviceResponse" + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + LastLocationTime: + description: Last date and time when the device was localized. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + type: string + example: "2023-09-07T10:40:52Z" + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + RetrieveLocationNotFound404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + summary: Identifier not found + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + RetrieveLocationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE + - LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE + - LOCATION_RETRIEVAL.UNABLE_TO_LOCATE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + summary: Missing identifier + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + summary: Unsupported identifier + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + summary: Unnecessary identifier + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + LOCATION_RETRIEVAL_422_UNABLE_TO_FULFILL_MAX_AGE: + summary: Unable to fulfill maxAge + description: The system is not able to provide the fresh location required by the client + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE + message: "Unable to provide expected freshness for location" + LOCATION_RETRIEVAL_422_UNABLE_TO_FULFILL_MAX_SURFACE: + summary: Unable to fulfill maxSurface + description: The system is not able to provide accurate acceptable surface required by the client + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE + message: "Unable to provide accurate acceptable surface for location" + LOCATION_RETRIEVAL_422_UNABLE_TO_LOCATE: + summary: Unable to locate device + description: The network cannot locate the device + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_LOCATE + message: "The network is unable to locate the device" + examples: + RETRIEVAL_CIRCLE: + summary: circle-based device location retrieval + description: The device is localized within a circle with a center at the specified coordinates and a radius of 800 meters. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + RETRIEVAL_POLYGON: + summary: polygon-based device location retrieval + description: The device is localized within a polygon delimited by the provided coordinates. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.752490 + longitude: 4.861876 + - latitude: 45.751224 + longitude: 4.861125 + - latitude: 45.751442 + longitude: 4.859827 + LOCATION_CIRCLE_WITH_DEVICE: + summary: circle-based device location retrieval, returning the device identifier used by the implementation + description: The device is localized within a circle with a center at the specified coordinates and a radius of 800 meters. Response when the request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + device: + phoneNumber: "+123456789" +``` diff --git a/marked/DeviceLocation/code/API_definitions/location-verification/raw.md b/marked/DeviceLocation/code/API_definitions/location-verification/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..15874822f017f4dd13337f1452bf0370d43e0b6d --- /dev/null +++ b/marked/DeviceLocation/code/API_definitions/location-verification/raw.md @@ -0,0 +1,692 @@ +# location-verification + +```yaml +openapi: 3.0.3 +info: + title: Device Location Verification + description: | + This API provides the consumer with the ability to verify the location of a device. + + # Introduction + + API consumers are able to verify whether the location of certain user device is within the area specified. Currently the only area supported as input is a circle determined by a set of coordinates (latitude and longitude) and some expected accuracy (radius). + + * If the provided area is out of the operator's coverage or it is not supported for any reason, an error `422 LOCATION_VERIFICATION.AREA_NOT_COVERED` will be returned. + * Legal restrictions regarding privacy, or other regulatory or implementation issues, may force the operator to set restrictions to the provided area, such as setting a minimum value to the accepted radius. In these cases, an error `422 LOCATION_VERIFICATION.INVALID_AREA` will be returned and the error message will refer to the reason of the limitation. + + The verification result depends on the network's ability and accuracy to locate the device at the requested area. + + * If the network's estimation of the device's location is fully contained within the requested area, the verification result is `TRUE`. + * If the network's estimation of the device's location does not overlap with the requested area at all, the verification result is `FALSE`. + * If the network's estimation of the device's location partially overlaps with the requested area, or it fully contains the requested area (because it is larger), the result is `PARTIAL`. In this case, a `match_rate` is included in the response, indicating an estimation of the likelihood of the match in percent. + * If the network cannot locate the device, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_LOCATE` is sent back. + * The client may optionally include a `maxAge` indication. If the location information known to the server is older than the specified `maxAge` or not known at all, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE` is sent back, independently of the verification result. + + Location Verification could be useful in scenarios such as: + + - Fraud protection, to ensure a given user is located in the location area claimed for financial transactions. + - Verification of GPS coordinates reported by the app on a device, to ensure the GPS was not faked, e.g. for content delivery with regional restrictions. + - Contextual-based advertising, to trigger advertising after verifying the device is in the area of interest. + - Smart mobility (vehicle / bikes renting), to confirm the location of the device and the location of the vehicle/bike to guarantee they are rented correctly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface where a device may be physically located. + + * **Max Age**: Maximum age of the location information which is accepted for the location verification (in seconds). + * Absence of maxAge means "any age" is acceptable for the client. In other words, this is like maxAge=infinite. In this case the system will return `lastLocationTime`. + * maxAge=0 means a fresh calculation is requested by the client. If the system is not able to provide the fresh location, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE` is sent back. + + + * **Verification**: Process triggered in the API server to confirm or contradict the expectation assumed by the API client about the device location. + + # API Functionality + + The API exposes a single endpoint/operation: + + - Verify whether the device location is within a requested area, currently a circle with center specified by the latitude and longitude, and radius specified by the accuracy. The operation returns a verification result and, optionally, a match rate estimation for the location verification in percent. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may response with: + + - an error indicating that that phone number is not supported for this API, or + - the verification for a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - a verification value that combines the location verification of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceLocation +servers: + - url: "{apiRoot}/location-verification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Location verification + description: Verification of the location of a device +paths: + /verify: + post: + tags: + - Location verification + summary: Verify the location of a device + description: | + Verify whether the location of a device is within a requested area. The operation returns a verification result and, optionally, a match rate estimation for the location verification in percent. + operationId: verifyLocation + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/VerifyLocationRequest" + examples: + INPUT_PHONE_NUMBER_CIRCLE: + summary: Phone number, circle and maxAge + description: Verify if device identified by a phone number is within a circle, providing a maxAge + value: + device: + phoneNumber: "+123456789" + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + INPUT_IP_ADDRESS_V4_CIRCLE: + summary: IPv4 address, circle, without maxAge + description: Verify if device identified by an IPv4 address is within a circle, not indicating a maxAge + value: + device: + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + INPUT_PHONE_NUMBER_IP_ADDRESS_V4_CIRCLE: + summary: Both phone number and IPv4 address, circle and maxAge + description: Verify if device identified both by a phone number and an IPv4 address is within a circle, providing a maxAge + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + INPUT_NO_DEVICE: + summary: Device not provided + description: The device has to be deducted from token + value: + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + responses: + "200": + description: Location verification result + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/VerifyLocationResponse" + examples: + VERIFICATION_TRUE: + summary: Match + description: The network locates the device within the requested area + value: + verificationResult: "TRUE" + lastLocationTime: "2023-09-07T10:40:52Z" + VERIFICATION_TRUE_WITH_DEVICE: + summary: Match returning the device identifier used by the implementation + description: The network locates the device within the requested area. Response when the request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + verificationResult: "TRUE" + lastLocationTime: "2023-09-07T10:40:52Z" + device: + phoneNumber: "+123456789" + VERIFICATION_FALSE: + summary: No match + description: The requested area does not match the area where the network locates the device + value: + verificationResult: "FALSE" + lastLocationTime: "2023-09-07T10:40:52Z" + VERIFICATION_PARTIAL: + summary: Partial match + description: The requested area partially matches the area where the network locates the device + value: + verificationResult: "PARTIAL" + matchRate: 74 + lastLocationTime: "2023-09-07T10:40:52Z" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/VerifyLocationNotFound404" + "422": + $ref: "#/components/responses/VerifyLocationUnprocessableEntity422" + security: + - openId: + - location-verification:verify +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + enum: + - CIRCLE + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: | + Expected accuracy for the verification, in meters from `center`. + Note: The area surface could be restricted locally depending on regulations. Implementations may enforce a larger minimum radius (e.g. 1000 meters). + minimum: 1 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + VerifyLocationRequest: + description: Request to verify the location of a device. Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + maxAge: + $ref: "#/components/schemas/MaxAge" + required: + - area + + VerifyLocationResponse: + description: Response to a location verification request + type: object + required: + - verificationResult + - lastLocationTime + properties: + verificationResult: + $ref: "#/components/schemas/VerificationResult" + lastLocationTime: + $ref: "#/components/schemas/LastLocationTime" + matchRate: + $ref: "#/components/schemas/MatchRate" + device: + $ref: "#/components/schemas/DeviceResponse" + + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the API provider might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different API providers. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + MaxAge: + description: The maximum age (in seconds) for the location known by the implementation, which is accepted for the verification. Absence of maxAge means "any age" and maxAge=0 means a fresh calculation. + type: integer + minimum: 0 + example: 120 + + VerificationResult: + description: | + Result of a verification request: + - `TRUE`: when the network locates the device within the requested area, + - `FALSE`: when the requested area does not match the area where the network locates the device, + - `PARTIAL`: when the requested area partially match the area where the network locates the device. A `match_rate` is included in the response. + type: string + enum: + - "TRUE" + - "FALSE" + - "PARTIAL" + + MatchRate: + description: Estimation of the match rate between the area in the request (R), and area where the network locates the device (N), calculated as the percent value of the intersection of both areas divided by the network area, that is (R ∩ N) / N * 100. Included only if VerificationResult is PARTIAL. + type: integer + minimum: 1 + maximum: 99 + + LastLocationTime: + description: Timestamp of the last location information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-09-07T10:40:52Z" + format: date-time + type: string + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + VerifyLocationNotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + VerifyLocationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - LOCATION_VERIFICATION.AREA_NOT_COVERED + - LOCATION_VERIFICATION.INVALID_AREA + - LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE + - LOCATION_VERIFICATION.UNABLE_TO_LOCATE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + LOCATION_VERIFICATION_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: LOCATION_VERIFICATION.AREA_NOT_COVERED + message: "Unable to cover the requested area" + LOCATION_VERIFICATION_422_INVALID_AREA: + summary: Invalid area + description: The requested area is too small to be supported by the system. + value: + status: 422 + code: LOCATION_VERIFICATION.INVALID_AREA + message: "The requested area is too small" + LOCATION_VERIFICATION_422_UNABLE_TO_FULFILL_MAX_AGE: + summary: Unable to fulfill maxAge + description: The system is not able to provide the fresh location required by the client + value: + status: 422 + code: LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE + message: "Unable to provide expected freshness for location" + LOCATION_VERIFICATION_422_UNABLE_TO_LOCATE: + summary: Unable to locate device + description: The network cannot locate the device + value: + status: 422 + code: LOCATION_VERIFICATION.UNABLE_TO_LOCATE + message: "The network is unable to locate the device" +``` diff --git a/marked/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3dba700f4190b272605761817beb418b96e27415 --- /dev/null +++ b/marked/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for geofencing-subscriptions 0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                  initial | public-release
                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/geofencing-subscriptions.yaml](/code/API_definitions/geofencing-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/geofencing-subscriptions.feature](/code/Test_definitions/geofencing-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/geofencing-subscriptions.feature](/code/Test_definitions/geofencing-subscriptions.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/ugHWB) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist/raw.md b/marked/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c2060da6bbfb5a51ad2f8e97149cf00aab9a8c22 --- /dev/null +++ b/marked/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for location-retrieval 0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                  initial | public-release
                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/location-retrieval.yaml](/code/API_definitions/location-retrieval.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/location-retrieval.feature](/code/Test_definitions/location-retrieval.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/location-retrieval.feature](/code/Test_definitions/location-retrieval.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AQBqBQ) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist/raw.md b/marked/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..45cca481216a76e622be32b5c8777ec7fdf7edf7 --- /dev/null +++ b/marked/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for location-verification 3.0.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                  initial | public-release
                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:--------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/location-verification.yaml](/code/API_definitions/location-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/location-verification-User-Story.md](/documentation/API_documentation/location-verification-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/location-verification.feature](/code/Test_definitions/location-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/location-verification.feature](/code/Test_definitions/location-verification.feature) | +| 9 | Test result statement | O | O | O | M | ? | https://github.com/camaraproject/DeviceLocation/issues/371 | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/F4BpBQ) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceLocation/documentation/API_documentation/location-verification-User-Story/raw.md b/marked/DeviceLocation/documentation/API_documentation/location-verification-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e785cf871a49625bb9c7ae64bb9b1ffc1666a4f8 --- /dev/null +++ b/marked/DeviceLocation/documentation/API_documentation/location-verification-User-Story/raw.md @@ -0,0 +1,11 @@ +# Location Verification API User Story + + +| **Item** | **Details** | +|------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------| +| ***Summary*** | As an enterprise application developer, I want to verify the location of a user's device, so that I can ensure the device is within a specified area for security and contextual-based services. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                  **Scope:**
                  - Verifies if the specified device is located within a predefined geographical area (e.g.circle with given coordinates and radius, polygon...). | +| ***Pre-conditions*** | The preconditions are listed below:
                  1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform.
                  2. The ASP:BusinessManager has successfully subscribed to the Location Verification API product from the product catalog via (or not) a Channel Partner.
                  3. The ASP:Administrator has onboarded the ASP:User to the platform.
                  4. The ASP:User performs an authorization request to CSP
                  5. The CSP checks access & End-User approval then provide access token to the ASP:User
                  6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API. | +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Location Verification API providing the End-User's device identifier (e.g., phone number), the area information (center coordinates and radius, polygon...) and the maximum age of the location information.
                    **Ends when:** The CSP's Location Verification server responds with the verification result indicating if the End-User's device is within the specified area, partially matches the area, or is unknown. When the device partially matches the area, the server additionally responds with a match-rate, which defines a percent value of the intersection of both areas. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the End-User's device location. | +| ***Exceptions*** | Several exceptions might occur during the Location Verification API operations
                    - Unauthorized: Invalid credentials (e.g., expired access token).
                    - Incorrect input data (e.g., malformed phone number).
                    - Not able to provide: Network unable to locate the device due to various reasons (e.g., device not connected, outdated location data). | diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17ead77005fea2792203e5f7d656995c6ea6b23e --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31/raw.md @@ -0,0 +1,44 @@ +# CAMARA DeviceLocation meeting - 2023-01-31 + +*January 31st, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Noel Wirzius (DT) +* Patrice Conil (Orange) +* Rafal Artych (DT) +* Robert Ludovic (orange) +* Udaka Kappagoda (Axiata Digital Labs) +* Vaibhav Metha () +* 정윤선님 Serena () + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introductions +* Overview of release management +* Review WoW for new proposals +* Open issues and PRs +* Noel from DT would like to present a couple of points +* TEF to propose enhancement of the response to cover partial matches +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Release management | Current version tagged as v0.1.0.
                    Versioning still being discussed in Commonalities.
                    We have a dev-v0.2.0 branch where new PRs are proposed, but other WGs are pulling PRs directly to main. | Waiting for decision on Commonalities and align with them | +| WoW | - First we should open a new issue to propose anything new. Get feedback and comments on issue.
                    - After some agreement, open a PR with details.
                    - To merge a PR we need at least 2 approvals, including Code Owners. | Reminder on the 'rules of engagement' | +| Add `maxAge` | [PR #9](https://github.com/camaraproject/DeviceLocation/pull/9) proposing new request parameter. Discussion on the PR still open | - Discussion of parameter position - should be in request/response?
                    - Tracking history of a location is not a API issue but related to network capabilities.
                    - UC: logistic to track shipment. Give access to people when they enter a building. Fraud tracking. Launching a app for a limited perimeter
                    - Reminder: this is not a 'precise' response as a minimum 2km radius is considered

                    **@Udaka triggers an issue & check with Geo fencing** | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12).
                    We must adapt errors and properties to guidelines | Waiting for decision on Commonalities and other WGs, and align with them | +| New points by DT | DT is currently working on an implementation against the nef and also I would love to discussss a new feature – subscription based tracking. | DT Improvements proposal:
                    - Subscription based (when a sim card enters a perimeter)
                    - Add a new response value for 'unknown'
                    - Get the cell location for a device

                    **@DT: Create new issue for each of them** | +| Covering partial matches (TEF) | [Issue TBC] Current response with a single boolean leaves some ambiguous scenarios where there are partial matches. | - How to manage partial matches as several 'in middle' scenarios are possible

                    **@José (Telefonica) opens an issue for this.** | + + +## AOB + +* Next call is on February 14th. \ No newline at end of file diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cc997646860e9f5bd5fca73fd328805a55c4a93c --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14/raw.md @@ -0,0 +1,35 @@ +# CAMARA DeviceLocation meeting - 2023-02-14 + +*February 14th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* José Luis Urien (Telefónica) +* Noel Wirzius (DT) +* Rafal Artych (DT) +* 若山 敏康 () + + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| YAML Update: add UNKNOWN for verify location | [PR #22](https://github.com/camaraproject/DeviceLocation/pull/22)
                    - Review if ready for merging | Pending on a second approval, **please @bigludo7 review** | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - New error format approved in Commonalities
                    - New model for `UeId` is being discussed in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG | - **@jlurien to create PR to align errors to new error model**

                    - Wait until discussions on new model for `UeId` are completed in QualityOnDemand and align with them | +| Enhancing response to cover partial matches | [Issue #20](https://github.com/camaraproject/DeviceLocation/issues/20)
                    - No feedback, so far. Discuss if ready for PR | - **@all Give feedback to issue** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18)
                    - No feedback, so far. Discuss if ready for PR | - **@all Give feedback to issue** | +| Add `maxAge` | Pending action from last meeting:

                    **@Udaka triggers an issue & check with Geo fencing** | - **@NoelWirzius to open new issue** | + + +## AOB + +* Next call is on February 28th. \ No newline at end of file diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..08457d2746125ab5fcc4995fe10ace6d5f3d4576 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14/raw.md @@ -0,0 +1,64 @@ +# CAMARA DeviceLocation meeting - 2023-03-14 + +*March 14th, 2023* + +## Attendees + +* Agustín Martín (Telefónica) +* Akos Hunyadi (DT) +* Inés Vidal (Telefónica) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Rafal Artych (DT) +* Robert Ludovic (Orange) +* Shuting Qing (Huawei) +* Tuan Tran (Broadpeak) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* WoW: PRs to main branch +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - New error format approved in Commonalities
                    - New model for `UeId` is being discussed in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. New terms agreed, pending to be submitted to Commonalities | - ~~**@jlurien to create PR to align errors to new error model**~~ [Merged](https://github.com/camaraproject/DeviceLocation/pull/28)

                    - Wait until discussions on new model for `UeId` are completed in QualityOnDemand and align with them.

                    - **Team OK with the change**| +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                    - Some feedback by Orange and Telefónica
                    - Some pending comments: Add DELETE and GET, support for susbcription termination due to consent removal (new event?) | - Valid enhancement from the team
                    - Need alignment & feedback with other API (topic raised in Commonalities)

                    - **Keep it open for further discussion** | +| Enhancing response to cover partial matches | [Issue #20](https://github.com/camaraproject/DeviceLocation/issues/20), [PR #31](https://github.com/camaraproject/DeviceLocation/pull/31)
                    - Feedback from Orange to make `matchRate` optional | - `matchRate` shifted to optional
                    - Let's see in future how we accommodate this attribute with future research (0-100; low, medium, high)

                    - **Team OK with the change** | +| Polymorphic Area | [Issue #26](https://github.com/camaraproject/DeviceLocation/issues/26), [PR #29](https://github.com/camaraproject/DeviceLocation/pull/29)
                    - New polymorphic model proposed. Only current `type = Circle` added
                    - Prepared for new types | - Add Elevation? Bring a clear UC and open another issue. Issue is to get the information from the network
                    - New types to be proposed, Telefónica to add Postcode, Orange to add polygon

                    - **Team OK with the change** | +| Path rename | [Issue #30](https://github.com/camaraproject/DeviceLocation/issues/30), [PR #35](https://github.com/camaraproject/DeviceLocation/pull/35)
                    - Proposal to rename path from `/verify` to `/verifications`, to align with guidelines
                    - Feedback from Orange and Telefónica | - **Team OK with the change** | +| Multiple devices per request | [Issue #32](https://github.com/camaraproject/DeviceLocation/issues/32), [PR #33](https://github.com/camaraproject/DeviceLocation/pull/33)
                    - Proposal to enable the location verification for multiple devices in one call.
                    - Feedback from Telefónica, Orange | - Discussion in progress in DT
                    - To be check if it is a bulk of 'autonomous' request or one business request with several UE
                    - Need a bulk mechanism -> This is point to raise to Commonalities

                    - **Keep it open for further discussion** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                    - Mentioned previously but new issue
                    - Feedback from Telefónica | - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered

                    - **Keep in open for further discussion** | +| WoW: PRs to main | - It was agreed in Commonalities to keep the latest changes in `main` branch, even if it is no a stable version
                    | - Proposal to merge current agreed PRs into `dev-0.2.0` branch, and then merge branch to `main` as version 0.2.0-wip
                    - Any pending PR to branch `dev-0.2.0` to be moved to `main`
                    - New PRs to be made to `main`

                    - **@jlurien to merge the PR for agreed today to main**, then we can add PR to main. | + + +## AOB + +* DT is currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. +

                    + +* Rafal raised the point about release management: + - 0.1 was released for MWC + - Right now we working on 0.2 + - We need to have an agreement around all API. +

                    + +* Joachim Dahlgren asked for device location (not check). + + - Tuan Tran (Broadpeak) supports the UC + - This is in the scope of this projet + - We probably need to have different endpoint, scope, etc… + - We need an issue to discuss. + - Sensitive from privacy but very relevant with B2B +

                    + +* Shuting asking about future roadmap on this API as today is only Device Location check + - Team indicated that the API will evolve in future with new capabilities +

                    + +* **Next call is on March 28th.** \ No newline at end of file diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7f8b0943a29632ef5b84d8d503b59661124f732c --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28/raw.md @@ -0,0 +1,54 @@ +# CAMARA DeviceLocation meeting - 2023-03-28 + +*March 28th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Shuting Qing (Huawei) +* Shyamal Patabendige () +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - **Keep waiting until proposal is merged in QoD** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                    - Some feedback by Orange and Telefónica
                    - Some pending comments: Add DELETE and GET, support for susbcription termination due to consent removal (new event?)
                    - Need alignment & feedback with other API (topic raised in Commonalities) | - Good progress in Commonalities
                    - Not far from the work done in Device location

                    - **Wait for outcome in Commonalities** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                    - Feedback from Telefónica
                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated | - Wait for clear requirement to complete model

                    - **Call for uses cases from the team, in particular for fresh information** | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39)
                    - Proposal by TEF to add Postal Codes as new type of area
                    - No feedback so far | - Discussion on the model, as other code could be used (like INSEE code in France)
                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.

                    - **Orange will provide information for France based on INSEE code** | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40)
                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                    - Proposal by Ericsson, feedback by DT and TEF | - Joachim: in our product we combine Device status & Device location.
                    - The use case is interesting. Get more details from Product teams
                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account.

                    - **Ludovic will raise an issue in Commonalities about "multiple endpoint API" vs "multiple API"** | + + +## AOB + +* Question from Shuting about architecture + - **Should be asked to Commonalities** + +* In last meeting, DT mentioned to be currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. + - **DT dev on NEF on hold** +

                    + +* In last meeting, Rafal raised the point about release management: + - 0.1 was released for MWC + - Right now we working on 0.2 + - We need to have an agreement around all API. + - Discussion on versioning. Proposal to change version each time we implement new code (each time we merge). DT mentioned that a Governance group is set up also to work on this topic, as right now is up to each sub projects. + - **We will decide on version update before merging new functionality.** +

                    + + +* **Next call is on April 11th.** \ No newline at end of file diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..dc25b5548df62d29d0e962488fd52fc443221e72 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11/raw.md @@ -0,0 +1,41 @@ +# CAMARA DeviceLocation meeting - 2023-04-11 + +*April 11th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - **Keep waiting until proposal is merged in QoD** (no progress in the last 2 weeks, as QoD was cancelled) | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                    - Some feedback by Orange and Telefónica
                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                    - Good progress in Commonalities
                    - Not far from the work done in Device location | - **Wait for outcome in Commonalities** (meeting planned April 12th with Akos & Pedro in order to close last comments - @Ludovic: hope to be able to make a proposal once validated by commonalities to device location) | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                    - Feedback from Telefónica
                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                    - Wait for clear requirement to complete model | - **Call for uses cases from the team, in particular for fresh information** (Need to figure out how it should work (DT) - Discussion also in Telefonica group)| +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                    - Proposal by TEF to add Postal Codes as new type of area
                    - Discussion on the model, as other code could be used (like INSEE code in France)
                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                    - Document that Circle is always supported | - No additional requirement from Orange on INSEE code used in France
                    - **New PR proposed by Telefonica.** OK from Ludovic (Orange), Akos will take a look for DT | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                    - Proposal by Ericsson, feedback by DT and TEF
                    - The use case is interesting. Get more details from Product teams
                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF |

                    - **Wait for more feedback from Commonalities**, and uses cases from Product teams | + + +## AOB + +* In last meeting, DT mentioned to be currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. + - **DT dev on NEF on hold. Bring topic back if status changes** +

                    + +* Rafal: need to clean some branches already merged. **@José will do.** +

                    + +* **Next call is on April 25th.** \ No newline at end of file diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7e3821047f3fa6521f2cc8c912d5ebbc2bd47fdb --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25/raw.md @@ -0,0 +1,48 @@ +# CAMARA DeviceLocation meeting - 2023-04-25 + +*April 25th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Asad Imran Aslam (Etisalat) +* Hacene Sali (Etisalat) +* Jamal Sahyoun (Etisalat ) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Ludovic Robert (Orange) +* Prashant Sidana (Etisalat) +* Rafal Artych (DT) +* Ravi Shekhar () +* Shuting Qing (Huawei) +* Syed Iqbal Hussain (Etisalat) +* Tarek Abu-Shaban (Etisalat) +* Toshi Wakayama (KDDI) +* Tuan Tran (Broadpeak) +* Wisam S Salim Najim () + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - QoD finally [merged changes, renaming `ueId` to `device`](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml)
                    - Wait for agreement on IP description
                    - **@jlurien will make a PR for this** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49)
                    - Some feedback by Orange and Telefónica
                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                    - New PR proposed to `main` branch by @maxl2287 (DT), as previous one [#27](https://github.com/camaraproject/DeviceLocation/pull/27) was closed | - Some agreement reached in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156)
                    - Still pending question about location
                    - **PR once agreed (Max or Ludovic)** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                    - Feedback from Telefónica
                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                    - Wait for clear requirement to complete model | - Last days for the comments for #34
                    - **@Akos will then make the PR** | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                    - Proposal by TEF to add Postal Codes as new type of area
                    - Discussion on the model, as other code could be used (like INSEE code in France)
                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                    - No additional requirement from Orange on INSEE code used in France |
                    - Alignment on country code terminology (from Akos review) - **@jlurien will update the PR**
                    - José reminds the business rational for adding postal code. All implementation must support circle area. All other area support is optional | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                    - Proposal by Ericsson, feedback by DT and TEF
                    - The use case is interesting. Get more details from Product teams
                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF and DT | - One or 2 APIs? Issue still open in Commonalities. From Telefonica & Orange preference to have 2 APIs on this UC to clearly separate check location from getting location. José rational for 2 APIs is to simplify release management. Joachim explained that from Ericsson they have separated in 2 APIs for security reason & distinct UC.
                    - **Get DT feedback on this specific API** if comfortable with 1 or 2 APIs.
                    - **@Ludovic can do a first PR for that once DT provide feedback**. We can have 2 yaml in API_definitions. Current yaml for location check need to be slightly revisited (naming, example, scope) | + + +## AOB + +* [PR #46](https://github.com/camaraproject/DeviceLocation/pull/46), related to [Issue #45](https://github.com/camaraproject/DeviceLocation/issues/45), merged and issue closed. + +* **Next call is on May 9th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c8dd335c281bdff0e357f6d7b48c0682519bd4af --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09/raw.md @@ -0,0 +1,77 @@ +# CAMARA DeviceLocation meeting - 2023-05-09 + +*May 9th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Ludovic Robert (Orange) +* Mohammad Sahid Khan () +* Prashant Sidana (Etisalat) +* Tarek Abu-Shaban (Etisalat) +* Shyamal Patabendige () +* Udaka Kappagoda (Axiata Group) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - QoD finally [merged changes, renaming `ueId` to `device`](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml)
                    - Wait for agreement on IP description. Still not resolved
                    - **@jlurien will make a PR for this** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49)
                    - Some feedback by Orange and Telefónica
                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                    - New PR proposed to `main` branch by @maxl2287 (DT), as previous one [#27](https://github.com/camaraproject/DeviceLocation/pull/27) was closed | - Good review discussion in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156), May 4th,2023
                    - Ludovic updated the guidelines accordingly. Now waiting for the merge in Commonalities
                    - **PR once agreed (Ludovic)** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                    - Feedback from Telefónica
                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                    - Wait for clear requirement to complete model | - New [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) by @hbujakow (DT)
                    - Same request than the one raised some time ago by Udaka Kappagoda
                    - We need to provide explanation how the parameters needs to work
                    - Documentation integration in OAS will be tracked in another PR
                    - Let's wait to get review for this PR specifically | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                    - Proposal by TEF to add Postal Codes as new type of area
                    - Discussion on the model, as other code could be used (like INSEE code in France)
                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                    - No additional requirement from Orange on INSEE code used in France
                    - José reminds the business rational for adding postal code. All implementation must support circle area. All other area support is optional |
                    - Alignment on country code terminology (from Akos review) - **@jlurien will update the PR**
                    - Some new comments on both issue and PR by @RogerJL. TEF keeps the PR on hold until better clarification on how to support partial implementations. Issue about the adoption because need support for other Telco. Probably we need to keep only the Circle right now. | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                    - Proposal by Ericsson, feedback by DT and TEF
                    - The use case is interesting. Get more details from Product teams
                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF and DT | - Akos (DT) - ok for this API to have 2 distinct API.
                    - **@Ludovic Ludovic will craft the swagger (not managing the subscription).** | + + +## AOB + +* [Issue #51](https://github.com/camaraproject/DeviceLocation/issues/51). Should we move parts of the schema shared by several projects to a common schema, such as `UeId`/`device`. Do we open an issue in Commonalities? + - We keep for now but the swagger must still be self-contained + - For ueId specifically we need always to be sync with other project. + - Have a common data dictionary will be definitely helpful but CAMARA is not yet at this stage +

                    + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. **@Jose to open poll** +

                    + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + - **@José will make it but after subscription is closed (and implemented)** +

                    + +## Other questions during meeting + +* Question about checking CAMARA API compliance ? + - There is no formal certification process right now --> nobody will check the code + - CAMARA is about the interface not the code to provide it --> Implementation has to align on the swagger definition. + - Example of issue on compliance: how to have a common behavior for MatchRate compute - there will be interpretation by implementation. + - Good topic for discussion in Commonalities --> Need an issue. +

                    + +* Comment about Partial answer + - Partial means the location match is no complete - but there will not additional response. This is not related to HTTP code 206. +

                    + +* Discussion about event subscription + - Geofencing probably will be in Check Location + - But we can imagine other subscription to get directly location (every 30 minutes for example). In this case in will be the Get location API. Right now we do not have requested for this later. +

                    + +* Question about authorization + - Several ways are defined but will be depending on local regulations + - Will be discussed case per case between consumer and provider + - This is beyond scope of this team +

                    + +* **Next call is on May 23th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..89f348ab608468641eed43aee9bf27e382c64734 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23/raw.md @@ -0,0 +1,103 @@ +# CAMARA DeviceLocation meeting - 2023-05-23 + +*May 23rd, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Hacene Sali (Etisalat) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefónica) +* Mohammad Sahid Khan () +* Rafal Artych (DT) +* Ravi Shekhar (ravishek) +* Syed Iqbal Hussain +* Tuan Tran (Broadpeak) +* 若山 敏康 () + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12) + +* New model for `ueId`/`device` defined in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand), including new model for IPv4Address. Already merged + +* **@jlurien will make a PR for this** Still pending + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + +* Discussed in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156) + - Ludovic updated the guidelines accordingly. Now waiting for the merge in Commonalities, pending on discussion for Guidelines versioning. + +* **PR once agreed (Ludovic)** -> Pending, Ludovic updated by email that he's ok with versioning proposal. + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Also [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related -> **@ukkaps to clarify** + +* Agreed to have a separate API from the current one + - Proposal to move current one to a new basePath, e.g. `device-location-verification`, and leave `device-location` to this new one + - **@jlurien to open issue to discuss new name** + +* Review PR by Ludovic + - Discussion about modelling endpoint as POST vs GET in [Commonalities Issue #212](https://github.com/camaraproject/WorkingGroups/issues/212) + - Seems there is consensus about using POST for use cases like this one + - Opinions, further comments on the PR? + - **@Ludovic Ludovic will modify the spec** | + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **@all, please provide comments to PR** + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** -> Pending + +### Units for radius + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. + +* **@Jose to open new issue** + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF keeps the PR on hold + +## AOB + +* Some questions about general topics of CAMARA, not directly related to Device Location. Pointing to the right place to raise that questions. + +* DT ask for time planning for new Release. Agreed to open an issue with tentative scope and roadmap, as they did in QoD. **AP on @jlurien** + +* Joachim comments about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - Current proposal is not clear about that + - **Joachim to open issue** + +

                    + +**Next call is on June 6th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4bcc538bfef957e3a0764fb306705dc93664deeb --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06/raw.md @@ -0,0 +1,135 @@ +# CAMARA DeviceLocation meeting - 2023-06-06 + +*June 6th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Asad Imran Aslam +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Ravi Shekar +* Sébastien Synold (Intersec) +* Shyamal Patabendige +* Toshi Wakayama (KDDI) +* Udaka Kappagoda (Axiata) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introduction to new members: Sébastien & Cetin +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12) + +* New model for `ueId`/`device` defined in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand), including new model for IPv4Address. + +* New PR #61 [https://github.com/camaraproject/DeviceLocation/pull/61]. Reviewed by Orange +* **Merge planned June 7th EOB if no blocking comment** + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + +* Discussed in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156) + - New model now consolidated in Guidelines. + - New [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/155) with a similar alignment to guidelines. It could be taken as example. + +* [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) by @maxl2287 (DT) needs to be adapted. * **DT will continue the crafting work** + +* Need discussion if Geo fence should be separated from check location operation as distinct model/business case could be provided. + - **Ludovic will create an issue to capture team feedback.** + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Agreed to have a separate API from the current one + - Proposal to move current one to a new basePath, e.g. `device-location-verification`, and leave `device-location` to this new one + - Issue [#59](https://github.com/camaraproject/DeviceLocation/issues/59). **To discuss during meeting** + +* Review PR by Ludovic + - Discussion about modelling endpoint as POST vs GET in [Commonalities Issue #212](https://github.com/camaraproject/WorkingGroups/issues/212) + - Seems there is consensus about using POST for use cases like this one + - Some comments and fixes in PR. + - Discussion in meeting about link with consent in particular when the location requested is for IoT - there is an Identity & Consent Management project where discussion occurs + +* **Merge planned June 7th EOB if no blocking comment.** + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **@all, please provide comments to PR** + - Need additional work to be completed as it is not 100% clear + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** +* **@Ludovic will make for the 'raw' location API** + +### Units for radius + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discuss during meeting: Depending on the back end - glmc (meter accuracy) or nef - the accuracy is very different + +* **Ask for team to provide comments in issue** + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No comments so far + - Discuss during meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider + +* **Ask for team to provide comments in issue** + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in June featuring + - For check location: + - Rename location to location-verification (issue 59) + - Align device model (PR 61) + - Add documentation in the OAS + - For raw location: + - Provide v0.1 + - With documentation integrated in the OAS + - Release in August + - Adding location subscription/notification for checking location + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF keeps the PR on hold. + +* **TEF will move discussion to business track in GSMA (@Jorge)** + +## AOB + + +

                    + +**Next call is on June 20th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ad85c1a171fe8065762f72eb1f51de24ea2d6ec7 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20/raw.md @@ -0,0 +1,140 @@ +# CAMARA DeviceLocation meeting - 2023-06-20 + +*June 20th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15) closed. +* [PR #61](https://github.com/camaraproject/DeviceLocation/pull/61) merged. + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + - To be aligned with Commonalities + - **DT will continue the crafting work** + +* [Issue #64](https://github.com/camaraproject/DeviceLocation/issues/64): Discussion if Geo fence should be separated from check location operation as distinct model/business case could be provided. + - **Team Decision**: We will have 2 APIS - Ludovic will comment issue & close it. + - Current Device location verification will stay only with one operation + - PR #49 should be close + - Need a discussion about the name + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Agreed to have a separate API from the current one + - [Issue #59](https://github.com/camaraproject/DeviceLocation/issues/59), [PR #66](https://github.com/camaraproject/DeviceLocation/pull/66) + - `device-location-verification` or `location-verification`: **Team Decision**: remove device prefix + +* Review PR by Ludovic + - **Team Decision**: need to switch to meter, related to [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discussion on age of location: + - Depends on the UC. If we do not provide age of location we need to have a global rule about retrieval delay + +* **Team Decision**: Regarding the date related parameters + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + +* Documentation will be handled in a second PR for raw location + +* Another API could be to have a history API but data are not obviously available from network. If needed, it is a separate use case. + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **Team Decision** Regarding the date related parameters: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) will be aligned. @José will comment +* @Ludovic will align raw location API + + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** -> Pending +* **@Ludovic will make for the 'raw' location API**, separate PR after [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +### Units for radius + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discuss during meeting: Depending on the back end - glmc (meter accuracy) or nef - the accuracy is very different + +* **Team decision**: Move to meters + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No comments so far + - Discuss during meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider + +* **Ask for team to provide comments in issue** + - Need to check how current system manage when the accuracy is to small - always False? + - Need additional discussion + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in June featuring + - For check location: + - Rename location to location-verification (issue 59) -> PR + - ~~Align device model (PR 61)~~ + - Add documentation in the OAS -> Pending PR + - For raw location: + - Provide v0.1 + - With documentation integrated in the OAS + - Release in August + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF has moved discussion to business track in GSMA. Any update? + - Not yet, @Jorge provides update on business track. + +## AOB + + +

                    + +**Next call is on July 4th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..10429c55e382e911da2e2dda08e8c5b69d444673 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04/raw.md @@ -0,0 +1,145 @@ +# CAMARA DeviceLocation meeting - 2023-07-04 + +*July 4th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Ravi Shekhar () +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + - PR #49 should be close, new PR to be created + - **DT will open new PR soon** + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - Orange preference for `location-verification-subscription` + - Keep open to get more opinions + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Review PR by @Orange: + - Switched to meters + - Added `maxAge` (optional) to request + - Added `lastLocationTime` (required) to response + - Documentation will be handled in a second PR for raw location + +* Almost ready - Ludovic will integrate José requests this week +* Align Area model with Location verification with allOf + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Agreed: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* Comments in [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53). It must be rebased, or close this and new PR + - ** @DT will discuss with the team how to process (rebase or new PR) ** +* Applied to [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* New [PR #71](https://github.com/camaraproject/DeviceLocation/pull/71), + - **ready to be merged** + + +### Units for radius + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Decided to move to meters. + - Pending new PR -> @TEF will do it, just converting to meters + +* Decide on new limits. Now, they are 2km to 200 km + - Discussion to set minimum to 1 km + - Privacy needs to be considered if we are too precise. + - Probably better for now to keep 2 km. + - Question from Joachim Dahlgren about correlation between precision vs consent required + - Question from Cetin about the max - Do we really need to set to 200 km explicitly + - We can remove it probably? + - ** AP: Open an Issue to discuss this. ** + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No new comments + - From previous meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider, need to check how current system manage when the accuracy is to small - always False? + +* To be discussed during meeting. + - ** @TEF will provide examples about 'Partial' UC ** + - We need to align on the formula to calculate the 'matchRate' for PARTIAL answer + + +### Align Area to new model for inheritance vs polymorphism + +* [Issue #72](https://github.com/camaraproject/DeviceLocation/issues/72) + - ** @TEF will open new PR ** + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in July featuring + - For check location: + - ~~Rename location to location-verification (issue 59)~~ + - ~~Align device model (PR 61)~~ + - Add documentation in the OAS -> PR to be merged + - For raw location: + - Provide v0.1 -> PR to be merged + - With documentation integrated in the OAS -> Pending PR + - Release in August / September (depending on holidays): + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* New request from GSMA to add administrative code (like postal code) + - How we will manage case where implementation did not provide all location type?, Discovery?, Error? + +* **@TEF: add a new issue and close this one.** + + +## AOB + +* Add a file for summer presence (Ludovic will do) + +

                    + +**Next call is on July 18th.** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..28e17386853ed14336e786c4d63de0dc937e1824 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18/raw.md @@ -0,0 +1,148 @@ +# CAMARA DeviceLocation meeting - 2023-07-18 + +*July 18th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Old PR #49 was close, new PR created + - Many comments, most resolved. Ongoing discussions in Commonalities may affect this PR. + - Probably better to **stick to current design** and then adjust later. + - DT team keeps the design aligned with Device Status API. + - Ludovic Robert will make a review of his previous comments to close resolved one + + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - Orange preference for `location-verification-subscription`, Ericsson preference for `geofencing` + - Joachim Dahlgren provided rational for geofencing instead of location-verification-subscription as we can have a second location subscription feature for geotracking. + - DT as owner of this API will consider this naming proposal and get back to the team (Akos Hunyadi) + - Looking for team feedback + + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Most comments resolved + - José Luis Urien Pinedo will make a final review + - Ludovic will work on the documentation only once PR#55 has been merged to avoid + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Agreed: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* Comments in [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53). It must be rebased, or close this and new PR + - ** @DT will discuss with the team how to process (rebase or new PR) ** -> José will check but the rebase has probably been already done +* Applied to [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No new comments + - From previous meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider, need to check how current system manage when the accuracy is to small - always False? + +* To be discussed during meeting. + - ** @TEF will provide examples about 'Partial' UC ** -> Some internal discussions, José will post some material to illustrate the problem; + - We need to align on the formula to calculate the 'matchRate' for PARTIAL answer + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in July featuring + - For check location: -> ready for 0.2 + - ~~Rename location to location-verification (issue 59)~~ + - ~~Align device model (PR 61)~~ + - ~~Add documentation in the OAS~~ + - For raw location: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - With documentation integrated in the OAS -> Pending PR + - Release in August / September (depending on holidays): + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* New request from GSMA to add administrative code (like postal code) + - How we will manage case where implementation did not provide all location type?, Discovery?, Error? + +* **@TEF: add a new issue and close this one.** -> Pending + +* Discussion on how to handle the 'diversity' of the 'geo' code that we can have in a given country. + +* How a developer will know the 'type' of area managed by a telco + - José mentioned discussion about TMF Catalog API (as operate API) - As a discovery feature. + - An error scenario must be defined in CAMARA if the area type requested is not supported by the telco + + +## Test Cases + +* New [Issue #80](https://github.com/camaraproject/DeviceLocation/issues/80) + +* Wait for other working group & commonalities agreement alignment + +* Discussion about use of Gherkin + specific implementation + - Gherkin file should (must?) be provided + - Specific language implementation file could be provided but as part of implementation contribution + + +## Accuracy Levels for Device Location APIs + +* New [Issue #78](https://github.com/camaraproject/DeviceLocation/issues/78) + - Discuss if we need this functionality + +* José/Ludovic not sure about the relevance of the problem with current technology as we're not able to provide 'fine-grain' location. + +* Joachim raised that if we have this capabilities to provide coarse vs fine we'll have a consent issue that cannot be at 'global' api level but dependent on the accuracy + + +## Summer 2023 presence + +* New [PR #75](https://github.com/camaraproject/DeviceLocation/pull/75) + - Only Ludovic added this presence + +* Keep Aug 1st - José will host. +* Skip Aug 15th …. except of someone volunteer to host it + + +

                    + +**Next call is on August 1st** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..64712ebf201289f4dbcba5cb454e75433cc71064 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01/raw.md @@ -0,0 +1,100 @@ +# CAMARA DeviceLocation meeting - 2023-08-01 + +*August 1st, 2023* + +## Attendees + +* Abhisek Das (Infosys) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Javier Carro (TEF) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Rafal Artych (DT) +* Toshi Wakayama (KDDI) +* Tuan Tran (Broadpeak) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Old PR #49 was close, new PR created + - Comments addressed, ready for final approval + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - `geofencing` got consensus as name, PR updated, issue closed + + +### New API to provide raw location, v0.1-wip + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Reviewed, has 2 approvals. Ready to be merged + - Ludovic will work on the documentation only once PR#55 has been merged to avoid + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - Discussion during meeting. Issue to be updated: + - Akos commented that the ratio may not be enough and maybe we should add some text or rational. + - Cetin thinks that it makes sense to return a low percent since it is caused by a bad behaviour of the network. + - Telefónica agrees but raise the problem with Product team approach and how the quality of the product is perceived. + - We will see the possibility to split the partial values into different values as proposed by Jose and Akos. + +### Roadmap for Release v0.2 + +* New [Issue #84](https://github.com/camaraproject/DeviceLocation/issues/84) to unify naming for POST operations + - Current one: POST /verifications + POST /retrieve-location + - Decide on POST /verify-location + POST /retrieve-location, or simpler: POST /verify + POST /retrieve + - **Agreed to change paths to POST /verify + POST /retrieve** + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. + +* Our roadmap could be: + - Release in August featuring + - For location-verification: -> ready for 0.2 + - For location: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - For geofencing: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - Release in late August / September (depending on holidays): + + +### Postal Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track, closing old [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39). [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) to be closed when new one is created. + +* Some initial comments, we can start discussion but this requirement will be in the scope of future releases. + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco + +* Requirement to be covered by future releases, we keep discussion open in issue. + + +## Summer 2023 presence + +* Decided to skip Aug 15th + + +## AOB + +* Akos raises the Commonalities Issue regarding CloudEvents and how it will affect the Geofencing API. + - From Telefónica, another colleague is working on the issue and will update Commonalities in the next days. + +

                    + +**Next call is on August 29th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8507a08cc6a87d819eda0667246983636308cb18 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29/raw.md @@ -0,0 +1,86 @@ +# CAMARA DeviceLocation meeting - 2023-08-29 + +*August 29th, 2023* + +## Attendees + +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Vidhi Mehta (Comviva) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Location Retrieval, v0.1-wip (Get raw location) + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Official name to be location-retrieval + - Reviewed, has 2 approvals. Decided to merge! + - Ludovic will work on the documentation only once PR#55 has been merged + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Ludovic provided feedback on notification discussion in Commonalities, progress & plan: + - Have a specific swagger for generic notification + - Format for this dedicated notification swagger --> probably use Cloud Event structure + - Use of callbacks clause in the API swagger to describe API notification + - Issue API Design for "Resource-based subscription", [Commonalities Issue #44](https://github.com/camaraproject/Commonalities/issues/44) is the good place to follow progress + - Some comments still pending + - Probably for next meeting we can align Geofencing with commonalities + - Close to be merged as v0.1.0-wip, inline doc to be added later + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53) +* Next steps: + - Create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, if aligned with Commonalities + - Give a couple of weeks for final testing and comments + - Approve a release after next meeting + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - Further discussion needed. Orange team will make a review. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) to be closed when new one is created. +* No new comments since last meeting, same questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. +* Discussion during the meeting: + - These questions could have a larger magnitude than this Device location API and should also infuse in Commonalities + - Adding Open Gateway product in the discussion could make sense as this OPGW could probably restrict a CAMARA API capability + - Discussion on the 'critical mass' to introduce API or API capability within one country. + + + +## AOB +N/A + +

                    + +**Next call is on September 12th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2a5e1e69ba17f8cbced91f5c79672bf14fbe52c5 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12/raw.md @@ -0,0 +1,93 @@ +# CAMARA DeviceLocation meeting - 2023-09-12 + +*September 12th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Fernando Prado Cabrillo (TEF) +* Javier Carro (TEF) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Location Retrieval, v0.1-wip (Get raw location) + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Merged but any comment are welcome + - Joachim: Maybe we should consider to send back other area than circle. +This is only in the response -> **@Joachim will raise an issue** + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Notification pattern is still in progress in Commonalities to accommodate use of [CloudEvents](https://github.com/camaraproject/Commonalities/pull/56) -> Once the model close in Commonalities should be quick to craft the API. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - PR still not merged, we should wait until Commonalities are approved. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + +* Joachim asked the question about consistence between the release name and the API name. + - Perhaps we can have a name for a family release + - Good topic to release in Commonalities -> **@Ludovic will raise an issue in Commonalities** + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* Discussion during meeting: + - Ludovic provided comment on José document + - The first point is to be aligned on the matchRate formulae. + - Both TEF & Orange feedbacks are that most of the result will be false or partial but very few chance to get True result. + - The problem is more significant if we allow 'small' scope (minimum radius) + - Good to keep in open + - **@Ludovic will fix the comment - should be matchRate no maxRate** + - Joachim: other alternative will be to answer the True/False but also the location + - This is not easy for Privacy issue + - We have the 'other' API to trigger this. + - Javier look on Ludovic proposal: could have worst result but in same time current approach did not cover all the case. + - After discussion seems that the team direction is to work on the PARTIAL answer and differentiate depending on the situation (see José document UC 3 & 4 for example). The PARTIAL answer could be completed with additional information + - **Think about improving PARTIAL information for next version** + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + +* No new comments since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                    + +**Next call is on September 26th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cef665e1ed331171602e8540994ca96a5a60f1e9 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26/raw.md @@ -0,0 +1,104 @@ +# CAMARA DeviceLocation meeting - 2023-09-26 + +*September 26th, 2023* + +## Attendees + +* José Luis Urien (TEF) +* Nicholas Venezia (centillion.ai) +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Akos Hunyadi (DT) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Jorge Garcia Hospital (TEF) +* Javier Carro Calador (TEF) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Notification pattern is still in progress in Commonalities to accommodate use of [CloudEvents](https://github.com/camaraproject/Commonalities/pull/56) -> Once the model close in Commonalities should be quick to craft the API. + - Discuss progress in commonalities but close to be merged + - José is OK and wait Pedro return to validate + - Shilpa validated + - Objective is to have the API ready for review for next meeting. + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Other possible areas other than circle + - Discuss which ones make sense: Polygon, Ellipse/EllipsoidArc, Areas including altitude? + - Positive feedback from Telefonica in particular for polygon in a first step. Orange shares this feedback for Polygon. + - José raised the point about multi-polygon + - Joachin mentionned used of GMLC + - **[question]** Question on how getting the altitude. + - **[action]** Check how the network how the polygon is described (set of points) and then we can craft the P/R to improve the API with this new feature. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [Draft PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, changing securitySchemes to openIdConnect. Waiting for resolution in Commonalities and Identity and Consent Management WGs. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Proposal to use date format, such as Release 2023-09, but no agreement so far. + - **[action]** José will check how this release management for a family is done within Edge API + - **[decision]** Without formal decision we will use the date & lead the path + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85), related to [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* Discussion during previous meeting: + - Need to align on the matchRate formulae. + - Problem with current proposal is that result will be false or partial but very few chance to get True result. The problem is more significant if we allow small areas as input. + - After discussion seems that the team direction is to work on the PARTIAL answer and differentiate depending on the situation (see José document UC 3 & 4 for example). The PARTIAL answer could be completed with additional information + - **Think about improving PARTIAL information for next version** + - Joachim had an internal review of the document - we have to write a document to explain how the matchRate is calculated. + - Discussion on the consent but probably not difference between retrieval & verification. + - The problem we have here for Location Verification will be also very significant for future geofencing API. + - Probably we need to have more maturity on this with some real implementation + - Nicholas Venezia provides feedback on how the Device location API is used within a podcast app to provide targeted ad. Nicholas demonstrated utilisation of location data. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + - Javier shared a proposal on this topic. + - **[Question]** How to map postal code to geolocation/coordinate? + - depending on the country - could be provided by local regulations + - Javier will share the proposal in the GIT. + +* No new comments or progress since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                    + +**Next call is on October 10th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ca0b836d3a83f517f93395f4b0d2a24bcc068eb6 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10/raw.md @@ -0,0 +1,114 @@ +# CAMARA DeviceLocation meeting - 2023-10-10 + +*October 10th, 2023* + +## Attendees + +* José Luis Urien (Telefonica) +* Foo Ming Hui (Singtel) +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Rafal Artych (DT) +* Akos Hunyadi (DT) +* Sébastien Synold (Intersec) +* Ludovic Robert (Orange) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Javier Carro Calador (Telefonica) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - New model based on CloudEvents are now approved + - PR proposed by DT https://github.com/camaraproject/DeviceLocation/pull/98 before the meeting. + - Ludovic raised the point about the event granularity - José shared the point and also expected 2 event types. + - Akos questionned if we need maxRate in this API. + - Cetin explained that in Vodafone implementation the cell id is used as an input. This will need API consumer to 'know' the cell which is a 'technical' information. + - [action] PR#74 could be close and point to PR#98 + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Other possible areas other than circle + - Discuss which ones make sense: Polygon, Ellipse/EllipsoidArc, Areas including altitude? + - Some comments on issue: + - OK to add polygon? + - Others? + + - José provided a feedback about TS29.572 review + - Limit to max 15 points could be challenged + - [action] Need PR for adding polygon as it is obvious. + - Need additional thinking for other area type + - Ludovic: What about adding the cell id ? + - José: It could be a way to discover the cell id but perhaps we could have a dedicated endpoint. + - [action] Worth to open an issue for this and think about it. + - Joachim : Need to verify if telco are willing to share this information. José: Perhaps using an alias could be an alternative. + - Discussion to be continued. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, changing securitySchemes to openIdConnect. Waiting for resolution in Commonalities and Identity and Consent Management WGs. + - Some approvals, can we merge? + - [Decision] Yes + - Joachim questionned about OIDC flows use-able. + - José/Ludovic answered that the proposal allow flexibilty by splitting the API yaml from the managed authorization for the API. This solution did not restriction authorization flow. In order to simplify adoption authorization flow must be constitent within one country + - [Action] : check for Device-location-retrieval and if not aligned to be tackled in next version. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + - geofencing has to be aligned with CloudEvents + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Proposal to use date format, such as Release 2023-09, but no agreement so far. + - EdgeCloud API using v1, v2 ... + - What name should we choose? + - [Decision] Let's wait for next TSC outcome. + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* No new comments +* Need a better name for Partial (Javier will work on it) + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + - Javier shared a proposal on this topic. + - **[Question]** How to map postal code to geolocation/coordinate? + - depending on the country - could be provided by local regulations + - [Action] Javier will share the proposal in the GIT. + +* No new comments or progress since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                    + +**Next call is on October 24th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3a0b9ea44e10409efa08221406f85e95e18a8d34 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24/raw.md @@ -0,0 +1,118 @@ +# CAMARA DeviceLocation meeting - 2023-10-24 + +*October 24th, 2023* + +## Attendees + +[x] José Luis Urien (Telefonica) +[] Foo Ming Hui (Singtel) +[x] Cetin Alpaycetin (Vodafone) +[x] Joachim Dahlgreen (Ericsson) +[x] Rafal Artych (DT) +[x] Akos Hunyadi (DT) +[] Sébastien Synold (Intersec) +[x] Ludovic Robert (Orange) +[x] Fernando Prado Cabrillo (Telefonica) +[] Jorge Garcia Hospital (Telefonica) +[] Javier Carro Calador (Telefonica) +[x] Ramesh Shanmugasundaram +[x] Amit Ajuha +[x] Parichaya Shrivastava + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Review last comments in PR + - Good progress - few comments left: + * Basepath should be enum and not default - Issue in Commonalities raised by José + * Move to openId for security schema + * Adding data in termination event + * Safer to include the information in the event body + + - Ludovic will update the commonalities on subscription/event after first usage in Device location, Device status & Sim Swap. + - Joachim raised the point about adding other area type --> will be done in future PR. + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Review last [PR #100](https://github.com/camaraproject/DeviceLocation/pull/100) adding polygon + - PR ready: + - limit to 15: OK for the team. + - [action] for Ludovic: + - Add precision about close shape in the documentation for polygon. This is not required to provide twiwe a point. + - Align with security schema (discussed in TSC but not finalized in the documentation) + - Align with basepath with an enum + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, already merged after discussion in TSC. + - Apply the same to location-retrieval and geofencing? + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Review discussion in TSC and agree on a name + - Discussed in TSC: + - DT will write a proposal on managing the proposal both for the API yaml(s) and family + - Have a global release for all CAMARA API for MWC 2024 + + +* Release content: + - location-verification v0.2-rc + - location-retrieval v0.1.0-wip + - geofencing v0.1.0-wip + - Changelog and Release notes. + +Points discussed: +* All this yaml will be under **0.2** family +* [action] For location-verification, José will fix the basepath with enum instead of default. + + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + +## AOB + +**Discussion on 3-legs pattern** raised by Joachim + * What is the third leg ? Is it always the flow going to the responsible 'party' for 'consent' grant? + * Let's take the example of a connected dog collar - The 'consent' should be provided by the user of the application tracking the dog. + * This management of the responsible 'party' for 'consent' grant is managed in the Authorization Server (AS). The AS for a given request for a device, a purpose and a data clain, compute the legal base and 'execute' it. Depending on the legal base there is not always a interaction with the responsible 'party' for 'consent' grant. + * Do we need to explictly provides in the request the device identifier as we can have it in the 'first leg'? + * This is relevant for some UC but we have UC where the Device A could trigger location request for another device. + * We mentioned the documentation provided in Identity&Consent management WG. + * We probably need to mention/point/refer this documentation in device location family API - We need to discuss how this information could be provided. + * The discussion will continue in following calls and depending on the work progress in Identity&Consent management WG. + +José will share the information to join the **Slack** + +

                    + +**Next call is on November 7th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2a3e5f2b017e5c8f50feeb867ccd68660a360ca3 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07/raw.md @@ -0,0 +1,93 @@ +# CAMARA DeviceLocation meeting - 2023-11-07 + +*November 7th, 2023* + +## Attendees + +- José Luis Urien (TEF) +- Joachim Dahlgreen (Ericsson) +- Jayant Nagaraj (Shabodi) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Nicholas Venezia (Centillion) +- Fernando Prado Cabrillo (TEF) +- Rafal Artych (DT) +- Ludovic Robert (Orange) +- Jorge Garcia Hospital (TEF) +- Javier Carro Calador (TEF) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + - Doc updated + - basePath fixed in URL + - Examples updated + - Decide what to do with IPV6 pattern + - José triggered an isue in QoD to discuss IPV6 format and then will align. José suggests to remove pattern if not fully correct (As of now this pattern did nort work for some subnet mask definition) + - We are waiting for QoD outcome on this point. + - Joachim suggested to raise an issue in Commonalitiesa we have to align this in every API as this is a generic topic + - Akos explained that we can merge even as rc because it is valid to still update rc + +* Review new README and CHANGELOG + - [PR #106](https://github.com/camaraproject/DeviceLocation/pull/106) + - Inspired by model in QoD + - *Links will work after branch for Release-0.2.0 is created* + - Discussion on versinning name and use of wip & rc suffix + - Location-Verification is in Alpha version + - Discussion if location-retrieval should be also in Alpha version. + - Geofencing shouldn't stay in pre-Alpha as there are not open issue (_note that pre-alpha is not a defined state_). Joachim explained that for him if it's wip then we do no code it (which is a fair argument to move geofencing to rc) + +* Release content: + - location-verification v0.2-rc + - location-retrieval v0.1.0-wip -> Do we keep -wip? + - We should create also a rc and align with current work for location verification. + - Decision: should be promoted to v0.1-rc + - **Ludovic (for Orange) will create a PR** + - geofencing v0.1.0-wip -> Do we keep -wip? + - Decision: should be promoted v0.1-rc + - **Max (for DT) will create a PR** + - Changelog and Release notes. + - **José asked the team to take a close look on PR#106 as this is what the external public will see.** + + - Akos suggests to create an issue for tracking and the 3 PR will refer this one. + +### New Issues + +* security and scopes for the Device Location API [#105](https://github.com/camaraproject/DeviceLocation/issues/105) + * --> Probably good to rout to identity & consent management project + +### Open discussions + +#### Behaviour when requesting too high precision + +_Not enough time to discuss_ + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + +## AOB + + +

                    + +**Next call is on November 21th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d544f30966ff1701cd49ea95b4beca000b1c09e8 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21/raw.md @@ -0,0 +1,114 @@ +# CAMARA DeviceLocation meeting - 2023-11-21 + +*November 21st, 2023* + +## Attendees + +- José Luis Urien (TEF) +- Javier Carro Calador (TEF) +- Nicholas Venezia (Centillion) +- Ben Thomas (Vodafone) +- Foo Ming Hui (SingTel) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Jorge Garcia Hospital (TEF) +- Ludovic Robert (Orange) +- Fernando Prado Cabrillo (TEF) +- Sébastien Synold (Intersec) +- Rafal Artych (DT) +- Surajj Jaggernath (Vodacom) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - Point about Ipv6 still open in QoD (will be valid for all three APIs) + - Description comment from Cetin to be considered + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - Error: Status & Code are 'normative' - message are open to modification by implementation + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - Rafal proposed to align Notification source example list accordingly to the guidelines + +We're still in line to release before the end of the year. + - Resolve pending comments and merge current PRs as -rc + - Open testing and feedback period for RC versions + + We need also to align with the new working group about release management + + First training Nov 21th + Rafal, Ludovic and José will attend + + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + +### Review other Issues and PRs + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Discussed during meeting + - To be discussed in Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + + - The team needs to be involved in this work + - Agreed to use Gherkin must we should have an alignement on the formal aspect + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - To be aligned with ongoing discussion and [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/237) + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + +* [Geofencing API - Semantic error](https://github.com/camaraproject/DeviceLocation/issues/109) + - Solved & closed + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Discuss during meeting + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +**[Decision]** Proposal is to use the formula defined in the Word document by Telefonica Team. + API documentation will be updated --> Add a document and have a link in each yaml to refer it. Telefonica will craft this document. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + + - Question from José if we need to keep this function in a same API or in a distinct one. + - This feature is not top priority right now but will be discused next year. + +Question about API certification from Ludovic + - Location retrieval is a good candidate + - topic links to the Test definition + - Let's wait for test definition outcomes and then we will assess use of this asset for certification purpose. + +## AOB + + +

                    + +**Next call is on December 5th** + José will be off - Fernando & Ludovic will host the call. diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..796197949823bd118be06cf8ef5961187c316c20 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05/raw.md @@ -0,0 +1,113 @@ +# CAMARA DeviceLocation meeting - 2023-12-5 + +*December 5th, 2023* + +## Attendees + + +- Ludovic Robert (Orange) +- Fernando Prado Cabrillo (TEF) +- Foo Ming Hui (SingTel) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Javier Carro (TEF) +- Rafal Artych (DT) +- Joachim Dahlgreen (Ericsson) +- Sönke Peters (Vodafone) +- Surajj Jaggernath (Vodacom) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs + * No new issue for last 2 weeks + * Cleaning for old issues +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - Point about Ipv6 solved + - Description comments from Cetin considered + - Precision on date time accordingly to the commonalities guidelines + - MERGED during the meeting + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - Point about Ipv6 solved (complete alignment with verification device structure) + - Ready to review + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - Rafal aligned Notification source example list accordingly to the guidelines + - Alignment with IP v6 to be done. + - Akos will align ip addresses and device model as has been done with location retrieval and location verification + - Typo found in "expiresAt" subscription info. Akos will fix. + + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + - No new comment since last meeting + +### Review other Issues and PRs + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - No progress + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - Aligned with ongoing discussion and [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/237) + - Done for Location retrieval & location verification + - To be done for geofencing + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Ludovic answered. + +* [Documentation Updated](https://github.com/camaraproject/DeviceLocation/issues/102) + - part of https://github.com/camaraproject/DeviceLocation/pull/104 + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - During previous meeting we agreed to use the formula defined in the Word document. + - Descriptions regarding partials and matchRate has been added in location-verification yaml + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + + +### Cleaning - issues closed +* [Does DeviceLocation itself really need to define all ways to identify a User equipment identifier](https://github.com/camaraproject/DeviceLocation/issues/51) - Tackled with https://github.com/camaraproject/DeviceLocation/issues/117 + +* [Include locationType as a request parameter](https://github.com/camaraproject/DeviceLocation/issues/43) - Request for Office/work location (most latched site/location in the day time) & Home location (most latched site/location in the night time). Managed in separate API request. + - Issue closed - Tackled with https://github.com/camaraproject/WorkingGroups/issues/336 + + [Accuracy Levels for Device Location APIs](https://github.com/camaraproject/DeviceLocation/issues/78) - nu update since July 31st José request for clarification to the issuer. + - Issue closed as there have been no updates in 3 months + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + + + +## AOB + + +

                    + +**Next call is on December 19th** diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..daba3b6487159fec6d5e4da51fc71414f8343038 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19/raw.md @@ -0,0 +1,117 @@ +# CAMARA DeviceLocation meeting - 2023-12-19 + +*December 19th, 2023* + +## Attendees +José Luis Urien Pinedo (Telefonica) +Ludovic Robert (Orange) +Surajj Jaggernath (Vodacom) +Cetin Alpaycetin (Vodafone) +Joachim Dahlgren (Ericsson) +Akos Hunyadi (DT) +Ravi Shekhar +Javier Carro Calabor (Telefonica) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/blob/main/code/API_definitions/location-verification.yaml) + - Already merged + - Minor fix merged: [Fix MaxAge type](https://github.com/camaraproject/DeviceLocation/pull/126) + - Any further comment/bug found? + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - PR approved + - Merged + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - PR approved + - Merged + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + - No new comment since last meeting + - José will take a last look and merge this PR. + +### Review other Issues and PRs + +#### New + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - José tested locally for location verification + - José plans to do same for the other APIs + - No major issue identified (only warning). + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Relevant question for possible enhancement. To be discussed. + - José took a look on google API implementation and they have a new input parameter to let client decide if she/he decide to get an event at subscription time. This is relevant only for entered area event. + - We can introduce a `initialTriggerAreaEntered` boolean - if it is true then a notification is sent if the mobile is within the area. + - Akos said that we can send the notification in every case (not requiring this attribute) + - Joachim raises the point about how we can distinct the fact that the device was already in the area vs it just entered in for this first event. + - A combination with Location retrieval could be also documented. Ludovic says that it can work except if the device just entered at subscription time. + - **We need to open an issue to discuss** about the compute rule for geofencing area match. We solved this for device verification API (for `matchRate`) but here this is different as it is dynamic. + - Recommendation to continue the discussion on the issue. + +#### From previous meeting + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - No progress + - DT Team has provided comment + - TEF team will also provide comments + - Discussion should continue in Commonalities + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - Already done, to be closed when merged + - **Closed** with PR merging. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Ludovic answered. + - **Closed** + +* [Documentation Updated](https://github.com/camaraproject/DeviceLocation/issues/102) + - part of https://github.com/camaraproject/DeviceLocation/pull/104 + - **Closed** with PR merging. + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - During previous meeting we agreed to use the formula defined in the Word document. + - Descriptions regarding partials and matchRate has been added in location-verification yaml + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + + +## AOB + +- Next call will be **January 16th, 2024** + +

                    + diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6e42b4374fd6d997a2320c95e4fa460bfc1b94ae --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16/raw.md @@ -0,0 +1,126 @@ +# CAMARA DeviceLocation meeting - 2024-01-16 + +*January 16th, 2024* + +## Attendees + +José Luis Urien Pinedo (Telefonica) +Joachim Dahlgren (Ericsson) +Akos Hunyadi (DT) +Cetin Alpaycetin (Vodafone) +Javier Carro Calador (Telefonica) +Ludovic Robert (Orange) +Nicholas Venezia (Centillion) +Jorge Garcia Hospital (Telefonica) +Foo Ming Hui (Singtel) +Fernando Prado Cabrillo (Tlefonica) + + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2-rc2 + +- Release Candidate was created in [branch](https://github.com/camaraproject/DeviceLocation/tree/release-0.2.0-rc) +- Error detected after releasing, with enum values for Area, [already fixed](https://github.com/camaraproject/DeviceLocation/issues/131) +- [Prepare RC2](https://github.com/camaraproject/DeviceLocation/pull/134) PR already merged +- New errors reported, to be fixed in RC2: + - [Correct YAML examples to use upper case enum of areaType](https://github.com/camaraproject/DeviceLocation/issues/136) + - Create PR with fix + + - [Fix format for attribute lastLocationTime in location retrieval](https://github.com/camaraproject/DeviceLocation/issues/137) + - Create PR with fix + + - [Rename in the OAS SubscriptionEventType to NotificationEventType](https://github.com/camaraproject/DeviceLocation/issues/139) + - Create PR to change schema names + +- Create RC2 branch and release tag + - Ludovic will do for both API + - No change for the version in the yaml + +### Review other Issues and PRs + +#### New + + - [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - Review comments + - José answers in the PR + - Joachim agreed on the fact that make sense to have one event type both for left & entered + - Akos: The UC is clear - how we solve it + - One approach is to allow to subscribe to an array of event type + - Discussed in the past but adding an array of notification type will add a layer of complexity to manage a subscription + - Could be a problem if the server is not able to manago one kind of event type. + - **Keep it open to let the discussion open.** + - José will also check with development team + - Having both 'event' in one notification type could have an impact on the server managing the event + + - [Revise Description to Meet GDPR Compliance - REMOVAL OF " Location-based advertising" in Documentation](https://github.com/camaraproject/DeviceLocation/issues/135) + - Review comments + - Nicholas will propose a better wording for this sentence + - Could be integrated in rc2 + + - [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - Review comments + - Need more review from the team + - Correlation with issue [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - **keep the discussion open** + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status + - Proposal to use this one as the 'model sample' for Commonalities + - **Keep in open but need to be prioritized** + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Next steps + - Integrate the linting in our CI as for QoD + - As codeowner we did not have the right to add it. + - José will comment and ping Markus & Rafal to ask them how we can move forward. + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Review comments, next steps + - Probably same thing must be done for area left. + - Akos & Ludovic have UC where it could be necessary. + - Nicholas mentionned also ad-based UC (ad in a podcast location-based for example) where we want to control the time when the ad should be triggered for a device + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open in Commonalities + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress in Commonalities + + +### Open discussions + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Next call will be **January 30th, 2024** + +

                    + diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..27e01f9979ed39d0c68b85d90f6ec528d3d39b2c --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30/raw.md @@ -0,0 +1,100 @@ +# CAMARA DeviceLocation meeting - 2024-01-30 + +*January 30th, 2024* + +## Attendees + +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Rafal Artych (DT) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2-rc2 + +- [PR](https://github.com/camaraproject/DeviceLocation/pull/142) with fixes to: + - [Correct YAML examples to use upper case enum of areaType](https://github.com/camaraproject/DeviceLocation/issues/136) + - [Fix format for attribute lastLocationTime in location retrieval](https://github.com/camaraproject/DeviceLocation/issues/137) + - [Rename in the OAS SubscriptionEventType to NotificationEventType](https://github.com/camaraproject/DeviceLocation/issues/139) + - [Revise Description to Meet GDPR Compliance - REMOVAL OF " Location-based advertising" in Documentation](https://github.com/camaraproject/DeviceLocation/issues/135) + +- AP: Give one more day for review, merge and create RC2 + +### Review other Issues and PRs + +#### New + + - [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Review comments. Cetin agrees with Ludovic's comment. + - AP: We'lll wait for Commonalities to add it to Geofencing. + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - Review new comments + - AP: Get more opinions. + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - Review new comments. + - AP: Get more opinions. + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - Review new comments + - AP: Wait for outcome in Commonalities + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - José asked Markus & Rafal how we can move forward. + - Rafal explains that process will be: + - Merge PR in commonalities with the initial ruleset as an artifact. + - Possibly a discussion in TSC about how to add it in each WG in a common way. + - AP: We'll wait for the process. In the meantime we are able to test it locally and provide feedback before integrating. + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - No new comments + - AP: We are at a point where we can create a PR. Jose will ping Akos in case he wants to create the PR, otherwise Jose will create it to move the discussion to the PR. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open in Commonalities. No new comments. + - AP: Ping in the issue to reactivate the discussion + +### Open discussions + +- No new comments since last meeting. We keep these discussions on hold. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Next call will be **February 13th, 2024** + +

                    + diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8f2504ef9c8ee65fbb6c850c333628e16e987540 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13/raw.md @@ -0,0 +1,143 @@ +# CAMARA DeviceLocation meeting - 2024-02-13 + +*February 13th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Javier Caaro Calabor (Telefonica) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2.0-rc3 + +- [PR](https://github.com/camaraproject/DeviceLocation/pull/150) with fixes to: + - [fix: correct $ref for SubscriptionEventType in geofencing](https://github.com/camaraproject/DeviceLocation/pull/149) + - Some other fixes and enhancements detected by linter (locally) + +- Give some time review, merge and create RC3 +- If nothing else is detected, then create release-0.2.0 + +Discussed during meeting: +Action: Team has to review the PR. We have to work offline to release the API before the MWC. +Minor typo fixes (on subscription) +Feedback on Linting tool run + + +### Review other Issues and PRs + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. -> Still pending + +Discussed during meeting: +- José explained that first we need to provide variable(s) + - First then 'given' to prepare this/these variable(s) + - Then the result with the expected responses + - +Additionnal step oculd be used (ad hoc for specific operation) +- GSMA will test this files as an input for Conformance & using Postman. +- José will contribut to commonalities for guidelines for Test Definition + - Ludovic agreed on José proposal and will adapt the Device location retrieval file once José made his proposal. + + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Positive feedback + - How to proceed? Create PR and share with Commonalities or the open issue in Commonalities? + +Discussed during meeting: +- Ludovic will create an Issue in Commonalities. + + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - No new comments + - Discuss next steps in meeting + +Discussed during meeting: +- we went through the proposal on the issue as 4 options are described +- We keep it open for discussion +- Alignement with device status was discussed. + + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - Discuss next steps in meeting + + Discussed during meeting: + - no progress - need team review + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - New [PR](https://github.com/camaraproject/Commonalities/pull/131) + - Review status + +Discussed during meeting: +- in final step in commonalities - soon to be applied + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Tested locally before creating RC3 + - Review status in Commonalities + +Discussed during meeting: +- Rafal provided a briefting of the situation + - Still in discussion in commonalities + - Question to TSC if each projet has to be independant for applying the lintening. + - else José will apply the CI in our project + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments + +Discussed during meeting: +- No comments + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - Recent comment to reactivate the discussion + +Discussed during meeting: +- Team has to provide comment +- Rafal mentionned another issue about duration + + +### Open discussions + +- No new comments since last meeting. + + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + +This item should be reopen after MWC. + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Discuss if we keep next call for February 27th, 2024, as it is the MWC week. + - We keep it + +

                    diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4a88d14db0d528406a293a81b7a1e9e5170ce0c1 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27/raw.md @@ -0,0 +1,115 @@ +# CAMARA DeviceLocation meeting - 2024-02-27 + +*February 27th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Rafal Artych (DT) +* Javier Caaro Calabor (Telefonica) +* Foo Ming Hu (Singtel) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Release 0.2.0 + + +- No new comments or bugs reported for [RC3](https://github.com/camaraproject/DeviceLocation/issues/155) + +- Discuss release approval + - **Agreed to release 0.2.0** + - AP @Jose: Create PR and make adjustments in Github. Remove RCs from Changelog if possible. + +### Review other Issues and PRs + +No new comments or progress on the ongoing issues and PRs + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. + - Update by Jose, but still pending + + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + + AP from previous meeting: + - Ludovic will create an Issue in Commonalities. -> Pending, double check with Ludovic + - Related issues in [DeviceStatus](https://github.com/camaraproject/DeviceStatus/issues/117) and QoD + + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + + Discussed during previous meeting: + - Alignement with device status was discussed. + + - No specific issue created so far in Commonalities, but mentioned in [issue](https://github.com/camaraproject/Commonalities/issues/140) about CloudEvents Subscription format. + - This is not an urgent issue as functionality can be covered with current events, so we may wait until discussions in Commonalities advance. + + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - Connected with [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85). A document with implementation guideline should cover this also. + + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - New [PR](https://github.com/camaraproject/Commonalities/pull/131) -> Still nor merged but seems to have all LGTM. AP: Double check with Ludovic + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Tested locally before creating RC3 + - Review status in [Commonalities](https://github.com/camaraproject/Commonalities/issues/142) + - AP @Rafal to propose a PR adding linting to our subproject CI + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments in the issue in the last 2 weeks + - Discussed during the meeting if we should wait for Commonalities for a common format, or add parameters in our current model nad adapt later to approved guidelines. + - As we are starting cycle for a new release, we can wait for the moment. Eventually, if we are about to release something new and commonalities are not agreed, we can tale the lead. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - No comments in the last 2 weeks + - Wait for outcome + +### Open discussions + +- No new comments since last meeting. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - [Document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal. + + This item should be reopen after MWC. + + - We should discussed approach on this for next release. Should we incorporate this to current operations, should we split this functionality to new endpoints or even separate APIs? + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + + - Joachim asked for plans or roadmap for R1.0 + - Jose commented that there is still no roadmap or time frame agreed for v1.0, but release plan for R1.0 should be agreed at CAMARA project level. + - At WG level we may discuss the content for next release, being 0.x or 1.x. So far we only have the requirement for Administrative Codes, but others may come from GSMA product track + +

                    + +- Next call will be on **March 12th, 2024** + +

                    + diff --git a/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12/raw.md b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..69507db2f5345c39f90572611dc337c0af265fa9 --- /dev/null +++ b/marked/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12/raw.md @@ -0,0 +1,138 @@ +# CAMARA DeviceLocation meeting - 2024-03-12 + +*March 12th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Joachim Dahlgren (Ericsson) +* Cetin Alpaycetin (Vodafone) +* Akos Hunyadi (DT) +* Javier Carro Calabor (Telefonica) +* Katrina Griese (Vodafone) +* Ludovic Robert (Orange) +* Alexander Boraczynski (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Rafal Artych (DT) +* Surajj Jaggernath (Vodacom) +* Toyeeb Rehman (GSMA) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + + +> [!IMPORTANT] +> [Release 0.2.0](https://github.com/camaraproject/DeviceLocation/releases/tag/v0.2.0) official!! +> +> New merges to be consolidated towards next -wip versions + + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### New + +#### Corrections + +* [[location-verification] Precise the description when matchRate needs to be set for PARTIAL-results](https://github.com/camaraproject/DeviceLocation/issues/158) + - Fixed in [PR 159](https://github.com/camaraproject/DeviceLocation/pull/159) + - Merged during the meeting. + +* [Add x-correlator as specified in the guideline](https://github.com/camaraproject/DeviceLocation/issues/160) + - PR to be created + - [Action] Ludovic will do + +* [subscriptionExpireTime is declared as "required" in the subscription-ends - note, but is optional currently](https://github.com/camaraproject/DeviceLocation/issues/161) +* Fixed along with old issue [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Fixed in [PR 163](https://github.com/camaraproject/DeviceLocation/pull/163) + - Merged during the meeting + +* [[Geofencing]: Invalid area example for POST /subscriptions](https://github.com/camaraproject/DeviceLocation/issues/164) + - Fixed in [PR 165](https://github.com/camaraproject/DeviceLocation/pull/165) + -Merged during the meeting + +* [Remove API from info.title](https://github.com/camaraproject/DeviceLocation/issues/169) + - Remove API from the title + - [Action] José will create the PR + - Could be part of the linter rule but not yet + - action to standardize the info object + +#### Documentation + +* [Should 501 NOT_IMPLEMENTED be returned for unimplemented DeviceLocation APIs?](https://github.com/camaraproject/DeviceLocation/issues/168) + - Question related to the conformance + - Team agreed with José & Cetin comments + - Toyeeb aggreed + - Issue closed + + +#### Ongoing + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - New PRs: [Introducing corrections for yamllint](https://github.com/camaraproject/DeviceLocation/pull/166) and [Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceLocation/pull/167) + - PR#166 Rafal will regenerate the linter & once done the PR will be merge + - PR#167: to be merged after #166 + - Can be done offline + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - New issue in Commonalities to discuss [Enhancement of the Testing Guidelines](https://github.com/camaraproject/Commonalities/issues/158) by TEF + - [Action] José propose to make an example to illustrate his proposal + - [Action] Toyeeb to check with GSMA conformance + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Ludovic will create an Issue in Commonalities. -> Pending, double check with Ludovic + - [Action] Yes Ludovic will create the PR in Commponalities + - Related issues in [DeviceStatus](https://github.com/camaraproject/DeviceStatus/issues/117) and QoD + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - New issue in Commonalities [Subscription-Issue2: Allow event consumers to subscribe to more than one event types with a single subscription](https://github.com/camaraproject/Commonalities/issues/154) + - Waiting for Commonalities outcomes + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments in the issue in the last 2 weeks + - Waiting for Commonalities outcomes + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - [Action] We need more comments from the team + - Connected with [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85). A document with implementation guideline should cover this also. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - No comments in the last 2 weeks + - Wait for outcome + +### Long term discussions + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - [Document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal. + + This item should be reopen after MWC. + + - We should discussed approach on this for next release. Should we incorporate this to current operations, should we split this functionality to new endpoints or even separate APIs? + - Need to be discussed + - Ludovic preference is for a separate API as for example in France this is not a request. + - For Javier this is not a top priority for Telefonica as of now. + - More generally probably we need to have feedback loop with GSMA team about API work (and review the priority as focus could change) + - Perhaps a point to be share in TSC. + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + - Joachim: Should be also aligned/synchronysed with Geofencing + +## AOB + +

                    + +- Next call will be on **March 26th, 2024** +- Easter week, but we keep the meeting + +

                    diff --git a/marked/DeviceLocation/documentation/SupportingDocuments/README/raw.md b/marked/DeviceLocation/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceLocation/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceMediaStreamingRate/README/raw.md b/marked/DeviceMediaStreamingRate/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ff5ed06db5a18506635b936411088e633a177a8a --- /dev/null +++ b/marked/DeviceMediaStreamingRate/README/raw.md @@ -0,0 +1,41 @@ + + + + + + + + + +# DeviceMediaStreamingRate + +Sandbox API Repository to describe, develop, document, and test the DeviceMediaStreamingRate API within the Sub Project [DeviceStatus](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/GQCbBQ) + +## Scope + +* Service API “DeviceMediaStreamingRate” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the customer with the ability to: + * Get insights about the network status of a defined mobile device. + * For this the API will return an indicator which is bundeling information about the device network status such as availibilty, open datavolume, congjestion, historical congjestion or the connecitvity status (2G, 3G, 4G, 5G). + * This API would be useful for applications that optimize user experience based on the connecitvity status of a defined device. +* Describe, develop, document, and test the APIs +* Started: August 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings or Sub Project Device Status are held virtually + * Schedule: Bi-weekly on Wednesday, 11:00 CET/CEST (08:00 UTC, 09:00 UTC during European DST) + * [Registration / Join]([https://wiki.camaraproject.org/x/TQAG](https://zoom-lfx.platform.linuxfoundation.org/meeting/94783050047?password=c43ff9fd-4c79-468a-9d98-45222dd6343d)) + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/DeviceStatus+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceMediaStreamingRate/code/API_definitions/README/raw.md b/marked/DeviceMediaStreamingRate/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/DeviceMediaStreamingRate/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate/raw.md b/marked/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..00cdfac9640958887fea04ed4e39ef94e76f285f --- /dev/null +++ b/marked/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate/raw.md @@ -0,0 +1,579 @@ +# media-streaming-rate + +```yaml +openapi: 3.0.3 +info: + title: Media Streaming Rate + version: wip + x-camara-commonalities: 0.6 + description: | + This is a media streaming rate service API that allows application developers to retrieve + the maximum media streaming bit rate supported for a given device. + + # Introduction + The Media Streaming Rate API allows an application developer to query the network + for the maximum supported media streaming bit rate for a specific end user device. + This API measures device connection quality by determining the maximum downstream + data rate available for media streaming, which is influenced by factors such as + network conditions, device capabilities, and current network congestion. + + This information helps developers ensure their media streaming applications can provide + optimal quality while using the current network connection, enabling adaptive bitrate + streaming and preventing buffering issues. + + # API functionality + + Prerequisite: authorisation and authentication + + Usage: + 1. Request: POST `retrieve-maximum-downstream-media-rate`, passing device identification + information such as IP address, phone number, or network access identifier. + 2. Response: The network will return the maximum downstream media streaming bit rate supported + for the device along with the unit of measurement. + + # Usage in Media Streaming Applications + + This API can be integrated into media streaming applications to determine optimal + video resolution for streaming. A typical workflow: + + 1. Application client requests manifest file (DASH/HLS) from CDN server + 2. Application client calls Media Streaming Rate API to get maximum supported bit rate + 3. Based on the response, application selects appropriate media resolution from the manifest + 4. Application begins media streaming from CDN using the optimal resolution + + This approach ensures the best possible viewing experience while preventing buffering or quality issues. + + The diagram below illustrates how the Media Streaming Rate API is used in a typical media streaming application: + + ![Media Streaming Rate API Sequence Diagram](../../documentation/SupportingDocuments/media-rate-sequence-flow.png) + + # Token usage: two-legged vs three-legged + + This API supports two types of access tokens: + + - **Two-legged token**: Used for server-to-server calls. The device to be queried MUST be identified by providing the `device` object in the request body. + - **Three-legged token**: Used for user-authenticated calls. The device is identified from the access token itself, and the `device` object MUST NOT be provided in the request. + + If a two-legged token is used and the device object is missing, the API will return a `422 MISSING_IDENTIFIER` error. + If a three-legged token is used and the device object is provided, the API will return a `422 UNNECESSARY_IDENTIFIER` error. + + This approach ensures clarity and security in device identification, and aligns with CAMARA API standards. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the device object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation + url: https://github.com/camaraproject/DeviceQualityIndicator + +servers: + - url: "{apiRoot}/media-streaming-rate/vwip" + variables: + apiRoot: + default: http://localhost:8087 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Media Streaming Rate + description: | + Retrieve the maximum media streaming bit rate supported for a given device. + +paths: + /retrieve-maximum-downstream-media-rate: + post: + security: + - openId: + - media-streaming-rate:retrieve-maximum-downstream-media-rate + tags: + - Media Streaming Rate + summary: Get maximum downstream media streaming rate + description: | + Retrieve the maximum downstream media streaming rate for a device. This helps application + developers determine the optimal media quality settings for their applications. + + When using a two-legged token, the device object MUST be provided. + When using a three-legged token, the device object MUST NOT be provided as + the device information will be extracted from the token. + operationId: retrieveMaximumDownstreamMediaRate + parameters: + - name: x-correlator + in: header + required: false + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + description: Device information needed to determine media rate capabilities. + content: + application/json: + schema: + $ref: "#/components/schemas/Device" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/MediaStreamingRateResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + +components: + securitySchemes: + openId: + type: openIdConnect + description: | + Common security scheme for all CAMARA APIs. + + Two types of tokens can be used with this API: + + 1. Two-legged token: Used for server-to-server calls where the device + information MUST be included in the request body. + + 2. Three-legged token: Used for user-authenticated calls where the device + information is extracted from the token itself. In this case, the + device object MUST NOT be included in the request. + + The specific authorization flows to be used will be agreed upon during + the onboarding process between the API consumer and the API provider. + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The + API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the same + device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + MediaStreamingRateResponse: + type: object + description: The maximum downstream media streaming bit rate supported for the device. + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + maxDownstreamMediaBitRateSupported: + type: integer + description: The maximum downstream bit rate supported for the device + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + type: string + description: The unit of the bit rate (e.g., Mbps, Kbps) + example: "Mbps" + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + required: + - maxDownstreamMediaBitRateSupported + - unit + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. +``` diff --git a/marked/DeviceMediaStreamingRate/documentation/API_documentation/README/raw.md b/marked/DeviceMediaStreamingRate/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceMediaStreamingRate/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceMediaStreamingRate/documentation/SupportingDocuments/README/raw.md b/marked/DeviceMediaStreamingRate/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceMediaStreamingRate/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceReachabilityStatus/README/raw.md b/marked/DeviceReachabilityStatus/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..863c362169d8c7646761a640247c962d3658538b --- /dev/null +++ b/marked/DeviceReachabilityStatus/README/raw.md @@ -0,0 +1,61 @@ + + + + + + + + + +# DeviceReachabilityStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceReachabilityStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mwD1Bg) + +## Scope + +* Service API(s) “DeviceReachabilityStatus” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if a device is reachable or is not connected to the network + * receive notifications if the connectivity status of the device changes +* Describe, develop, document, and test the API(s) +* Started: July 2022 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) +* Incubating stage since: February 2025 (via DeviceStatus) + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DeviceReachabilityStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **device-reachability-status-subscriptions v0.8.0** + [[YAML]](https://github.com/camaraproject/DeviceReachabilityStatus/blob/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + * **device-reachability-status v1.1.0** + [[YAML]](https://github.com/camaraproject/DeviceReachabilityStatus/blob/r1.2/code/API_definitions/device-reachability-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceReachabilityStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceReachabilityStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceReachabilityStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md b/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f764a3fd3f5bba98b752fdc762697db177917420 --- /dev/null +++ b/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md @@ -0,0 +1,1778 @@ +# device-reachability-status-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Reachability Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Reachability status events. + + # Introduction + + ## Reachability Status + API consumer is able to be notified whether the reachability status of a certain user device has changed to either data- or sms-usage. + This capability is provided via a subscription request - in this case the reachability situation is part of the event notification, which is sent back to the event subscriber when reachability situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes following capability: + + ## Device reachability status subscription + + These endpoints allow to manage event subscription on reachability device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data``: Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms``: Event triggered when the device is connected to the network only for SMS usage + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected``: Event triggered when the device is not connected. + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** reachability state of the device: + + | subscribed event-type | device reachability status at subscription time | event sent if ``initialEvent`` set to true | Explanation | + | ----------------------| ------------- | --------------- | ---------------| + | reachability-data | Device can use data | Yes | The device is reachable for data, so the event is triggered. | + | reachability-data | Device is disconnected or SMS-only | No | The device cannot use data, so no event is sent. | + | reachability-sms | Device can use data | No | The device can use data, but for thids event is only for SMS. | + | reachability-sms | Device is SMS-only | Yes | The device supports SMS, so the event is triggered. | + | reachability-sms | Device is disconnected | No | The device cannot send SMS, so no event is send. | + | reachability-disconnected | Device can use data or SMS usage | No | The device is reachable, so no "disconnected" event is sent. | + | reachability-disconnected | Device is disconnected | Yes | The device is disconnected, so the event is triggered. | + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which reachability status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide reachability status update notifications for the multi-SIM group as a whole, or + - provide reachability status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceReachabilityStatus + +servers: + - url: "{apiRoot}/device-reachability-status-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Device reachability status subscription + description: Operation to manage event subscription on device reachability status event. + +paths: + /subscriptions: + post: + tags: + - Device reachability status subscription + summary: "Create a device reachability status event subscription for a device" + description: Create a device reachability status event subscription for a device + operationId: createDeviceReachabilityStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device reachability status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + reachability-data: + $ref: "#/components/examples/REACHABILITY_DATA" + reachability-sms: + $ref: "#/components/examples/REACHABILITY_SMS" + reachability-disconnected: + $ref: "#/components/examples/REACHABILITY_DISCONNECTED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device reachability status subscription + summary: "Retrieve a list of device reachability status event subscription" + description: Retrieve a list of device reachability status event subscription(s) + operationId: retrieveDeviceReachabilityStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-reachability-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device reachability status subscription + summary: "Retrieve a device reachability status event subscription for a device" + operationId: retrieveDeviceReachabilityStatusSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device reachability status subscription + summary: "Delete a device reachability status event subscription for a device" + operationId: deleteDeviceReachabilityStatusSubscription + description: Delete a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer subscribes to reachability SMS. If consumer sets initialEvent to true and device is already reachable by SMS, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage. + + reachability-disconnected - Event triggered when the device is not connected. + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends. + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data: "#/components/schemas/EventReachabilityData" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms: "#/components/schemas/EventReachabilitySms" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected: "#/components/schemas/EventReachabilityDisconnected" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + If the time of the occurrence cannot be determined then this attribute MAY be set to some other time (such as the current time) by the CloudEvents producer, + however all producers for the same source MUST be consistent in this respect. In other words, + either they all use the actual time of the occurrence or they all use the same algorithm to determine the value used. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2018-04-05T17:31:00Z" + + EventReachabilityData: + description: event structure for reachability data usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilitySms: + description: event structure for reachability SMS usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilityDisconnected: + description: event structure for disconnection + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + ReachabilityDataSmsDisconnected: + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnded: + description: Event structure for sending subscription-ended event + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + SubscriptionEnded: + description: Event detail structure for org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + REACHABILITY_DATA: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_SMS: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_DISCONNECTED: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a device reachability status subscription ends. + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-22T05:40:23.682Z" + + SUBSCRIPTION_STARTED: + description: The cloud event when a device reachability status subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a device reachability status subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] +``` diff --git a/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status/raw.md b/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..21ef77a9b75c4c50c3e6c5015d5e44ffa5926f7e --- /dev/null +++ b/marked/DeviceReachabilityStatus/code/API_definitions/device-reachability-status/raw.md @@ -0,0 +1,559 @@ +# device-reachability-status + +```yaml +openapi: 3.0.3 +info: + title: Device Reachability Status + description: | + This API provides the API consumer with the ability to query device reachability status. + + # Introduction + + ## Reachability Status + + API consumer is able to verify whether a certain user device is reachable from the network via data- or sms-usage. + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Reachable:** Indicates, if the device is reachable from the network or not. + + * **Connectivity:** Indicates the connectivity types (DATA, SMS or both) through which the device is reachable from the network. + + * **LastStatusTime** : The time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ### Device Reachability situation + + The endpoint `POST /retrieve` allows to get current connectivity status information synchronously. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the reachability status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined reachability status for the multi-SIM group as a whole, or + - return the reachability status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceReachabilityStatus + +servers: + - url: "{apiRoot}/device-reachability-status/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Device reachability status + description: Operations to get the current reachability status of a device +paths: + /retrieve: + post: + tags: + - Device reachability status + summary: "Get the current reachability status information" + description: Get the current reachability status information + operationId: getReachabilityStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RequestReachabilityStatus" + required: true + responses: + "200": + description: Contains information about current reachability status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ReachabilityStatusResponse" + examples: + Reachable Using SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Reachable Using SMS With Device Disambguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Reachable Using Data: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA"] + Reachable Using Data and SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA", "SMS"] + Not Reachable Over The Mobile Network: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: false + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + LastStatusTime: + description: | + The last time that the device reachability status was confirmed to be correct by the API provider. The status should still be valid, but the API provider is unable to confirm this. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ReachabilityStatusResponse: + type: object + required: + - lastStatusTime + - reachable + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + reachable: + description: Indicates overall device reachability + type: boolean + connectivity: + type: array + items: + $ref: "#/components/schemas/ConnectivityType" + + ConnectivityType: + description: | + DATA: The device is connected to the network for Data usage (regardless of the SMS reachability) + + SMS: The device is connected to the network only for SMS usage + + type: string + enum: + - DATA + - SMS + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + RequestReachabilityStatus: + description: The request to retrieve the current reachability status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue +``` diff --git a/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4a9b8d91c3f065063f090cdb0d5df80b11965821 --- /dev/null +++ b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md @@ -0,0 +1,25 @@ +# API Readiness Checklist + +Checklist for device-reachability-status 1.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-reachability-status.yaml](/code/API_definitions/device-reachability-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [device-reachability-status-User-Story.md](/documentation/API_documentation/device-reachability-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | See [here](https://github.com/camaraproject/DeviceReachabilityStatus/issues/44) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | See (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/2wHWB) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..758aff37e7ae4b095315df5d4d329f6d413a133c --- /dev/null +++ b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md @@ -0,0 +1,20 @@ +# Device Reachability Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the reachability status of a user's device, so that I can determine whether the device is reachable via SMS, data (mobile internet), or both, enabling better communication or service management decisions based on real-time device availability. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                    **Scope:** Order To Activate (OTA) - Get connectivity status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the reachability status of a user's device | M | +| Ends when | The service provider returns the reachability status of the device with a timestamp when the status information was updated. In case of the device is reachable, additionally, the type of the connectivity (data, sms or both) is returned as well. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                    - Unauthorized: Invalid credentials (e.g., expired access token).
                    - Incorrect input data (e.g., malformed phone number).
                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) diff --git a/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..404147a358c391def01bb844c5783e9cab8779cf --- /dev/null +++ b/marked/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for device-reachability-status-subscriptions 0.8.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-reachability-status-subscriptions.yaml](/code/API_definitions/device-reachability-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-reachability-status-subscriptions.feature](/code/Test_definitions/device-reachability-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/JAFmBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceReachabilityStatus/documentation/SupportingDocuments/README/raw.md b/marked/DeviceReachabilityStatus/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceReachabilityStatus/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceRoamingStatus/README/raw.md b/marked/DeviceRoamingStatus/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..edbaef5fb6fa4b97612d64ea354110c90234ade1 --- /dev/null +++ b/marked/DeviceRoamingStatus/README/raw.md @@ -0,0 +1,61 @@ + + + + + + + + + +# DeviceRoamingStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceRoamingStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/127729674/DeviceRoamingStatus) + +## Scope + +* Service API(s) “DeviceRoamingStatus” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if a device is roaming, and in which country + * receive notifications if the roaming status of the device changes +* Describe, develop, document, and test the API(s) +* Started: July 2022 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DeviceRoamingStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **device-roaming-status-subscriptions v0.8.0** + [[YAML]](https://github.com/camaraproject/DeviceRoamingStatus/blob/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + * **device-roaming-status v1.1.0** + [[YAML]](https://github.com/camaraproject/DeviceRoamingStatus/blob/r1.2/code/API_definitions/device-roaming-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceRoamingStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceRoamingStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceRoamingStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md b/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3d053c973e03fba14d7782371ea34f6d03fa5bcf --- /dev/null +++ b/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md @@ -0,0 +1,1862 @@ +# device-roaming-status-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Roaming Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Roaming status events. + + # Introduction + + ## Roaming Status + API consumer is able to be notified whether the roaming status of a certain user device has changed. + This capability is provided via a subscription request - in this case the roaming situation is not in the response but event notification is sent back to the event subscriber when roaming situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes following capability: + + ## Device roaming status subscription + + These endpoints allow to manage event subscription on roaming device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `type` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status`` - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on`` - Event triggered when the device switch from roaming OFF to roaming ON + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off``: Event triggered when the device switch from roaming ON to roaming OFF + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country``: Event triggered when the device in roaming change country code + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** roaming state of the device: + + | subscribed event-type | device roaming status at subscription time | event sent if ``initialEvent`` set to true | + | ----------------------| ------------- | --------------- | + | roaming-status | Roaming On | Yes | + | roaming-status | Roaming Off | Yes | + | roaming-on | Roaming On | Yes | + | roaming-on | Roaming Off | No | + | roaming-off | Roaming On | No | + | roaming-off | Roaming Off | Yes | + | roaming-change-country | Roaming Off | No(*) | + | roaming-change-country | Roaming On | No(*) | + + (*) Use of ``initialEvent`` has no impact on roaming-change-country event-type. + + **Clarification on ``roaming-change-country`` event-type:** + + ``roaming-change-country`` event is sent only when the device stays in roaming situation and change country. + Suppose a device from Germany & all event types subscribed: + + - Device moves from Germany to France: + - triggered: roaming-status & roaming-on + - not triggered: roaming-change-country & roaming-off + - Device moves from France to Belgium: + - triggered: roaming-change-country + - not triggered: roaming-status, roaming-on & roaming-off + - Device moves from Belgium back to Germany + - triggered: roaming-status & roaming-off + - not triggered: roaming-on & roaming-change-country + + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which roaming status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide roaming status update notifications for the multi-SIM group as a whole, or + - provide roaming status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceRoamingStatus + +servers: + - url: "{apiRoot}/device-roaming-status-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device roaming status subscription + description: Operation to manage event subscription on device roaming status event. + +paths: + /subscriptions: + post: + tags: + - Device roaming status subscription + summary: "Create a device roaming status event subscription for a device" + description: Create a device roaming status event subscription for a device + operationId: createDeviceRoamingStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device roaming status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + roaming-status: + $ref: "#/components/examples/ROAMING_STATUS" + roaming-change-country: + $ref: "#/components/examples/ROAMING_CHANGE_COUNTRY" + roaming-on: + $ref: "#/components/examples/ROAMING_ON" + roaming-off: + $ref: "#/components/examples/ROAMING_OFF" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device roaming status subscription + summary: "Retrieve a list of device roaming status event subscription" + description: Retrieve a list of device roaming status event subscription(s) + operationId: retrieveDeviceRoamingStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-roaming-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device roaming status subscription + summary: "Retrieve a roaming status event subscription for a device" + description: retrieve device roaming status subscription information for a given subscription. + operationId: retrieveDeviceRoamingStatusSubscription + security: + - openId: + - device-roaming-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device roaming status subscription + summary: "Delete a device-roaming-status event subscription for a device" + operationId: deleteDeviceRoamingStatusSubscription + description: Delete a given device-roaming-status subscription by ID + security: + - openId: + - device-roaming-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: device-roaming-status subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the current Commonalities version (v0.5) only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status: "#/components/schemas/EventRoamingStatus" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country: "#/components/schemas/EventRoamingChangeCountry" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off: "#/components/schemas/EventRoamingOff" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on: "#/components/schemas/EventRoamingOn" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventRoamingStatus: + description: event structure for roaming status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingStatus" + + EventRoamingOn: + description: event structure for roaming on change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingOff: + description: event structure for roaming off change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingChangeCountry: + description: event structure for roaming change country + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingChangeCountry" + + EventSubscriptionEnded: + description: Event structure for sending subscription-ended event + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + RoamingStatus: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - roaming + properties: + roaming: + type: boolean + description: Roaming status. True, if it is roaming. + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + RoamingChangeCountry: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + - countryName + properties: + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + SubscriptionEnded: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + required: + - terminationReason + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ROAMING_STATUS: + value: + id: "123654" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + roaming: true + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-17T13:18:23.682Z" + + ROAMING_OFF: + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-18T13:18:23.682Z" + + ROAMING_ON: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + ROAMING_CHANGE_COUNTRY: + value: + id: "123657" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + countryCode: 214 + countryName: ["ES"] + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a device roaming status subscription ends. + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_STARTED: + description: The cloud event when a device roaming status subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a device roaming status subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] +``` diff --git a/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status/raw.md b/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c4ffda2e2246e808a1857956df938d84f4b8828a --- /dev/null +++ b/marked/DeviceRoamingStatus/code/API_definitions/device-roaming-status/raw.md @@ -0,0 +1,596 @@ +# device-roaming-status + +```yaml +openapi: 3.0.3 +info: + title: Device Roaming Status + description: | + This API provides the API consumer with the ability to query device roaming Status + + # Introduction + + ## Roaming Status + API consumer is able to verify whether a certain user device is in roaming situation (or not). + + The verification of the roaming situation depends on the network's ability. Additionally to the roaming status, when the device is in roaming situation, visited country information could be returned in the response. + + ## Possible Use-Cases + Roaming status verification could be useful in scenario such as (not exhaustive): + - For regulatory reasons, where a customer may need to be within a certain jurisdiction, or out with others, in order for transactions to be authorized + - For security / fraud reasons, to establish that a customer is located where they claim to be + - For service delivery reasons, to ensure that the customer has access to particular service, and will not incur roaming charges in accessing them + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Roaming** : Roaming status - `true`, if device is in roaming situation - `false` else. + + * **Country** : Country code and name - visited country information, provided if the device is in roaming situation. + + * **LastStatusTime** : The time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ## Device roaming situation + + The endpoint `POST /retrieve` allows to get roaming status and country information (if device in roaming situation) synchronously. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the roaming status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined roaming status for the multi-SIM group as a whole, or + - return the roaming status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceRoamingStatus + +servers: + - url: "{apiRoot}/device-roaming-status/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Roaming status retrieval + description: Operation to get device roaming status and country information (if roaming) synchronously +paths: + /retrieve: + post: + tags: + - Roaming status retrieval + summary: "Get the current roaming status and the country information" + description: Get the current roaming status and the country information + operationId: getRoamingStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusRequest" + examples: + INPUT_PHONE_NUMBER: + summary: Phone number + description: Retrieve roaming status for a device identified by a phone number + value: + device: + phoneNumber: "+123456789" + INPUT_IP_ADDRESS_V4: + summary: IPv4 address + description: Retrieve roaming status for a device identified by an IPv4 address + value: + device: + ipv4Address: + publicAddress: "123.234.1.2" + publicPort: 1234 + INPUT_IP_ADDRESS_V6: + summary: IPv6 address + description: Retrieve roaming status for a device identified by an IPv6 address + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + INPUT_NO_DEVICE: + summary: Device not provided + description: The device has to be deducted from token + value: + {} + required: true + responses: + "200": + description: Contains information about current roaming status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusResponse" + examples: + Not Roaming: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: false + No Country Name: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 901 + countryName: [] + Single Country Code: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Single Country Code With Device Disambiguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Multiple Country Names: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 340 + countryName: ["BL", "GF", "GP", "MF", "MQ"] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + RoamingStatusResponse: + type: object + required: + - lastStatusTime + - roaming + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + roaming: + $ref: "#/components/schemas/ActiveRoaming" + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + LastStatusTime: + description: | + The last time that the device roaming status was confirmed to be correct by the API provider. It might not be possible to provide the current status because, for example, the device may not be connected to any mobile network. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ActiveRoaming: + description: Roaming status. True, if it is roaming + type: boolean + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + RoamingStatusRequest: + description: The request for retrieving the current roaming status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue +``` diff --git a/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4a759050fd9b1ae96f45ad4dc46417aba6514752 --- /dev/null +++ b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md @@ -0,0 +1,25 @@ +# API Readiness Checklist + +Checklist for device-roaming-status 1.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-roaming-status.yaml](/code/API_definitions/device-roaming-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [device-roaming-status-User-Story.md](/documentation/API_documentation/device-roaming-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | See [here](https://github.com/camaraproject/DeviceRoamingStatus/issues/46) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | See (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/vYBmBQ) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f3c0c1c784bcaafac2854b02da435e58b848f969 --- /dev/null +++ b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md @@ -0,0 +1,21 @@ +# Device Roaming Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the roaming status of a user's device, so that I can determine whether a device is in a foreign network and in which country it is located. This API can be used to identify fraud, ensure regulatory compliance, or enforce territorial restrictions on video and audio content. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                    **Scope:** Order To Activate (OTA) - Get roaming status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the roaming status of a user's device | M | +| Ends when | The service provider returns the roaming status of the device with a timestamp when the status information was updated. In case of a roaming situation also the roaming country name and code shall be returned. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                    - Unauthorized: Invalid credentials (e.g., expired access token).
                    - Incorrect input data (e.g., malformed phone number).
                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) + diff --git a/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c1eba010a9db4632f18d6fcccf21abd92b526bcc --- /dev/null +++ b/marked/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for device-roaming-status-subscriptions 0.8.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-roaming-status-subscriptions.yaml](/code/API_definitions/device-roaming-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-roaming-status-subscriptions.feature](/code/Test_definitions/device-roaming-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/D4FlBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceRoamingStatus/documentation/SupportingDocuments/README/raw.md b/marked/DeviceRoamingStatus/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceRoamingStatus/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceStatus/README/raw.md b/marked/DeviceStatus/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4948d61fc35a8432e5de7ced5fe70b1abeb11fe2 --- /dev/null +++ b/marked/DeviceStatus/README/raw.md @@ -0,0 +1,82 @@ + + + + + + + + + +# DeviceStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +> [!WARNING] +> After the Camara Spring25 meta release this repository has been separated into 3 individual repositories: +> - [Device Roaming Status](https://github.com/camaraproject/DeviceRoamingStatus) +> - [Device Reachability Status](https://github.com/camaraproject/DeviceReachabilityStatus) +> - [Connected Network Type](https://github.com/camaraproject/ConnectedNetworkType) +> +> This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + +## Scope +* Service APIs for “Device Status” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + - check if a device is reachable or is not connected to the network + - check if a device is roaming, and in which country + - receive notifications if the connectivity or roaming status of the device changes +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/DeviceStatus/releases/tag/r2.2) (Spring25), with the following API versions: + * **connected-network-type-subscriptions v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml) + * **connected-network-type v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/connected-network-type.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type.yaml) + * **device-reachability-status-subscriptions v0.7.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + * **device-reachability-status v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-reachability-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status.yaml) + * **device-roaming-status-subscriptions v0.7.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + * **device-roaming-status v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-roaming-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-dst. + * A message to the community of this Sub Project can be sent using . + diff --git a/marked/DeviceStatus/code/API_definitions/connected-network-type-subscriptions/raw.md b/marked/DeviceStatus/code/API_definitions/connected-network-type-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8bf0dc4c026ba4e6432c4b02916a286cc2a6b95c --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/connected-network-type-subscriptions/raw.md @@ -0,0 +1,1501 @@ +# connected-network-type-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Connected Network Type Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to notifications on changes to the connected network type of a device. + + # Introduction + + ## Connected Network Type Subscription + API consumers can subscribe to receive notifications when the connected network type of a device changes. These notifications are delivered through CloudEvents. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Connected Network Type**: This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`: if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`: if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`: if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`: if device is connected to the 5G network technology + - `UNKNOWN`: if connection [technology] can not be determined + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type Subscription Management + + These endpoints allow you to manage subscriptions for receiving notifications on changes to the connected network type of a device. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed``: This event is triggered when the connected network type of the device changes. + + Note: Additionally, the event `org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + When ``initialEvent`` is set to ``true`` in the subscription request, a notification has to be sent immediately to provide the connected network type of the device targeted. + Note: If the status can not be determined, or if the device is not connected, we send an inital event with ``connectedNetworkType`` valued to`UNKNOWN`. + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding connected network type can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which connected network type notifications should be generated. If the phone number is used as the device identifier when creating a subscription in a multi-SIM scenario, the API may: + - respond with an error, or + - generate network type change notifications for the multi-SIM group as a whole, or + - generate network type change notifications for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/connected-network-type-subscriptions/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Connected Network Type Subscription + description: Operations to manage subscriptions for receiving notifications on changes to the connected network type of a device. + +paths: + /subscriptions: + post: + tags: + - Connected Network Type Subscription + summary: "Create a subscription for receiving notifications on changes to the connected network type of a device" + description: Create a subscription for receiving notifications on changes to the connected network type of a device. + operationId: createConnectedNetworkTypeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever the connected network type of the device changes. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + network-type-changed: + $ref: "#/components/examples/NETWORK_TYPE_CHANGED" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created (Successful creation of subscription) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a list of device connected network type event subscription" + description: Retrieve a list of device connected network type event subscription(s) + operationId: retrieveConnectedNetworkTypeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a device connected network type event subscription for a device" + description: retrieve ConnectedNetworkType subscription information for a given subscription ID. + operationId: retrieveConnectedNetworkTypeSubscription + security: + - openId: + - connected-network-type-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Subscription Details: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connected Network Type Subscription + summary: "Delete connected network type event subscription for a device" + operationId: deleteConnectedNetworkTypeSubscription + description: delete a given ConnectedNetworkType subscription. + security: + - openId: + - connected-network-type-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: ConnectedNetworkType subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + description: The error info object for possible error cases + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ConnectedNetworkType: + type: string + description: Network Type is intended to provide insight to connected network's capabilities from standards perspective. Actual network capabilities may differ based on implementation and MUST be checked with the connected network provider. + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed: "#/components/schemas/EventNetworkTypeChange" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventNetworkTypeChange: + description: event structure for network type change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/EventNetworkTypeChangeData" + + EventNetworkTypeChangeData: + description: Event detail structure for network type changed data events + type: object + required: + - connectedNetworkType + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + SubscriptionEnds: + description: Event detail structure for SUBSCRIPTION_ENDS event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + NETWORK_TYPE_CHANGED: + description: The cloud event when a connected network type changed + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + specversion: "1.0" + datacontenttype: application/json + data: + subscriptionId: "987654321" + device: + phoneNumber: "+123456789" + connectedNetworkType: 5G + time: "2023-03-22T05:40:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends" + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } +``` diff --git a/marked/DeviceStatus/code/API_definitions/connected-network-type/raw.md b/marked/DeviceStatus/code/API_definitions/connected-network-type/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d9b545a21bbb8c1660ec1c44427e48f48a7c851a --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/connected-network-type/raw.md @@ -0,0 +1,496 @@ +# connected-network-type + +```yaml +openapi: 3.0.3 +info: + title: Connected Network Type + description: | + This API provides the customer with the ability to query to which Mobile Communication Technology it is connected to. + + # Introduction + + ## Connected Network Type + + The API consumer is able to query the device's connected network type. The API provider can determine this in various ways. For example, the network type can be inferred from the specific radio cell to which the device is connected, as radio cells only support a single technology. It is important to note that the API does not query the device directly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. + + * **Connected Network Type** : This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`, if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`, if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`, if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`, if device is connected to the 5G network technology + - `UNKNOWN` if connection [technology] can not be determined + + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type + + The endpoint `POST /retrieve` allows to get connected Network Type. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which the connected network type should be returned. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a common connected network type for the multi-SIM group as a whole, or + - return the connected network type for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/connected-network-type/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Connected Network Type + description: Operations to get the network type device is connected to +paths: + /retrieve: + post: + tags: + - Connected Network Type + summary: "Get the connected network type" + description: Get the connected network type to which the user device is connected + operationId: getConnectedNetworkType + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - connected-network-type:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeRequest" + required: true + responses: + "200": + description: Contains connected network type + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeResponse" + examples: + Connected-to-4G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected-to-5G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 5G + Connected-to-Undetermined: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: UNKNOWN + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + LastStatusTime: + description: Last time that the associated connected Network Type was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ConnectedNetworkTypeResponse: + type: object + required: + - connectedNetworkType + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + + ConnectedNetworkType: + description: | + * UNKNOWN: Used when connection [technology] can not be determined + * 2G: 2nd Generation Mobile Communication Technology + * 3G: 3rd Generation Mobile Communication Technology + * 4G: 4th Generation Mobile Communication Technology + * 5G: 5th Generation Mobile Communication Technology + + type: string + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ConnectedNetworkTypeRequest: + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md b/marked/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..631f87c403c1745c600ff55e568bc25150e5a688 --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions/raw.md @@ -0,0 +1,1606 @@ +# device-reachability-status-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Reachability Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Reachability status events. + + # Introduction + + ## Reachability Status + API consumer is able to be notified whether the reachability status of a certain user device has changed to either data- or sms-usage. + This capability is provided via a subscription request - in this case the reachability situation is part of the event notification, which is sent back to the event subscriber when reachability situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + # API Functionality + + The API exposes following capability: + + ## Device reachability status subscription + + These endpoints allow to manage event subscription on reachability device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data``: Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms``: Event triggered when the device is connected to the network only for SMS usage + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected``: Event triggered when the device is not connected. + + Note: Additionally to these list, ``org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** reachability state of the device: + + | subscribed event-type | device reachability status at subscription time | event sent if ``initialEvent`` set to true | Explanation | + | ----------------------| ------------- | --------------- | ---------------| + | reachability-data | Device can use data | Yes | The device is reachable for data, so the event is triggered. | + | reachability-data | Device is disconnected or SMS-only | No | The device cannot use data, so no event is sent. | + | reachability-sms | Device can use data | No | The device can use data, but for thids event is only for SMS. | + | reachability-sms | Device is SMS-only | Yes | The device supports SMS, so the event is triggered. | + | reachability-sms | Device is disconnected | No | The device cannot send SMS, so no event is send. | + | reachability-disconnected | Device can use data or SMS usage | No | The device is reachable, so no "disconnected" event is sent. | + | reachability-disconnected | Device is disconnected | Yes | The device is disconnected, so the event is triggered. | + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which reachability status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide reachability status update notifications for the multi-SIM group as a whole, or + - provide reachability status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-reachability-status-subscriptions/v0.7" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Device reachability status subscription + description: Operation to manage event subscription on device reachability status event. + +paths: + /subscriptions: + post: + tags: + - Device reachability status subscription + summary: "Create a device reachability status event subscription for a device" + description: Create a device reachability status event subscription for a device + operationId: createDeviceReachabilityStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device reachability status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + reachability-data: + $ref: "#/components/examples/REACHABILITY_DATA" + reachability-sms: + $ref: "#/components/examples/REACHABILITY_SMS" + reachability-disconnected: + $ref: "#/components/examples/REACHABILITY_DISCONNECTED" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device reachability status subscription + summary: "Retrieve a list of device reachability status event subscription" + description: Retrieve a list of device reachability status event subscription(s) + operationId: retrieveDeviceReachabilityStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-reachability-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device reachability status subscription + summary: "Retrieve a device reachability status event subscription for a device" + operationId: retrieveDeviceReachabilityStatusSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + subscription-activation-requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + subscription-deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device reachability status subscription + summary: "Delete a device reachability status event subscription for a device" + operationId: deleteDeviceReachabilityStatusSubscription + description: Delete a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer subscribes to reachability SMS. If consumer sets initialEvent to true and device is already reachable by SMS, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data: "#/components/schemas/EventReachabilityData" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms: "#/components/schemas/EventReachabilitySms" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected: "#/components/schemas/EventReachabilityDisconnected" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + If the time of the occurrence cannot be determined then this attribute MAY be set to some other time (such as the current time) by the CloudEvents producer, + however all producers for the same source MUST be consistent in this respect. In other words, + either they all use the actual time of the occurrence or they all use the same algorithm to determine the value used. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2018-04-05T17:31:00Z" + + EventReachabilityData: + description: event structure for reachability data usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilitySms: + description: event structure for reachability SMS usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilityDisconnected: + description: event structure for disconnection + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + ReachabilityDataSmsDisconnected: + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + SubscriptionEnds: + description: Event detail structure for org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + REACHABILITY_DATA: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_SMS: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_DISCONNECTED: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-22T05:40:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } +``` diff --git a/marked/DeviceStatus/code/API_definitions/device-reachability-status/raw.md b/marked/DeviceStatus/code/API_definitions/device-reachability-status/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5fc2087cbeef9af93561b21b280787e8539af0e4 --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/device-reachability-status/raw.md @@ -0,0 +1,535 @@ +# device-reachability-status + +```yaml +openapi: 3.0.3 +info: + title: Device Reachability Status + description: | + This API provides the API consumer with the ability to query device reachability status. + + # Introduction + + ## Reachability Status + + API consumer is able to verify whether a certain user device is reachable from the network via data- or sms-usage. + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Reachable:** Indicates, if the device is reachable from the network or not. + + * **Connectivity:** Indicates the connectivity types (DATA, SMS or both) through which the device is reachable from the network. + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ### Device Reachability situation + + The endpoint `POST /retrieve` allows to get current connectivity status information synchronously. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the reachability status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined reachability status for the multi-SIM group as a whole, or + - return the reachability status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 1.0.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-reachability-status/v1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Device reachability status + description: Operations to get the current reachability status of a device +paths: + /retrieve: + post: + tags: + - Device reachability status + summary: "Get the current reachability status information" + description: Get the current reachability status information + operationId: getReachabilityStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RequestReachabilityStatus" + required: true + responses: + "200": + description: Contains information about current reachability status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ReachabilityStatusResponse" + examples: + Connected-With-SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Connected-With-DATA: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA"] + + Connected-With-DATA-And-SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA", "SMS"] + Not-Reachable: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: false + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + LastStatusTime: + description: Last time that the associated device reachability status was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + ReachabilityStatusResponse: + type: object + required: + - reachable + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + reachable: + description: Indicates overall device reachability + type: boolean + connectivity: + type: array + items: + $ref: "#/components/schemas/ConnectivityType" + ConnectivityType: + description: | + DATA: The device is connected to the network for Data usage (regardless of the SMS reachability) + + SMS: The device is connected to the network only for SMS usage + + type: string + enum: + - DATA + - SMS + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + RequestReachabilityStatus: + description: The request to retrieve the current roaming-status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue +``` diff --git a/marked/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md b/marked/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8a06c28d24d9e17d42466ab9a8089c0b2cb360f1 --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions/raw.md @@ -0,0 +1,1713 @@ +# device-roaming-status-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Device Roaming Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Roaming status events. + + # Introduction + + ## Roaming Status + API consumer is able to be notified whether the roaming status of a certain user device has changed. + This capability is provided via a subscription request - in this case the roaming situation is not in the response but event notification is sent back to the event subscriber when roaming situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + # API Functionality + + The API exposes following capability: + + ## Device roaming status subscription + + These endpoints allow to manage event subscription on roaming device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `type` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status`` - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on`` - Event triggered when the device switch from roaming OFF to roaming ON + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off``: Event triggered when the device switch from roaming ON to roaming OFF + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country``: Event triggered when the device in roaming change country code + + Note: Additionally to these list, ``org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** roaming state of the device: + + | subscribed event-type | device roaming status at subscription time | event sent if ``initialEvent`` set to true | + | ----------------------| ------------- | --------------- | + | roaming-status | Roaming On | Yes | + | roaming-status | Roaming Off | Yes | + | roaming-on | Roaming On | Yes | + | roaming-on | Roaming Off | No | + | roaming-off | Roaming On | No | + | roaming-off | Roaming Off | Yes | + | roaming-change-country | Roaming Off | No(*) | + | roaming-change-country | Roaming On | No(*) | + + (*) Use of ``initialEvent`` has no impact on roaming-change-country event-type. + + **Clarification on ``roaming-change-country`` event-type:** + + ``roaming-change-country`` event is sent only when the device stays in roaming situation and change country. + Suppose a device from Germany & all event types subscribed: + + - Device moves from Germany to France: + - triggered: roaming-status & roaming-on + - not triggered: roaming-change-country & roaming-off + - Device moves from France to Belgium: + - triggered: roaming-change-country + - not triggered: roaming-status, roaming-on & roaming-off + - Device moves from Belgium back to Germany + - triggered: roaming-status & roaming-off + - not triggered: roaming-on & roaming-change-country + + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which roaming status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide roaming status update notifications for the multi-SIM group as a whole, or + - provide roaming status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-roaming-status-subscriptions/v0.7" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device roaming status subscription + description: Operation to manage event subscription on device roaming status event. + +paths: + /subscriptions: + post: + tags: + - Device roaming status subscription + summary: "Create a device roaming status event subscription for a device" + description: Create a device roaming status event subscription for a device + operationId: createDeviceRoamingStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device roaming status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + roaming-status: + $ref: "#/components/examples/ROAMING_STATUS" + roaming-change-country: + $ref: "#/components/examples/ROAMING_CHANGE_COUNTRY" + roaming-on: + $ref: "#/components/examples/ROAMING_ON" + roaming-off: + $ref: "#/components/examples/ROAMING_OFF" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device roaming status subscription + summary: "Retrieve a list of device roaming status event subscription" + description: Retrieve a list of device roaming status event subscription(s) + operationId: retrieveDeviceRoamingStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-roaming-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device roaming status subscription + summary: "Retrieve a roaming status event subscription for a device" + description: retrieve device roaming status subscription information for a given subscription. + operationId: retrieveDeviceRoamingStatusSubscription + security: + - openId: + - device-roaming-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + subscription-activation-requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + subscription-deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device roaming status subscription + summary: "Delete a device-roaming-status event subscription for a device" + operationId: deleteDeviceRoamingStatusSubscription + description: Delete a given device-roaming-status subscription by ID + security: + - openId: + - device-roaming-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: device-roaming-status subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the current Commonalities version (v0.5) only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + NotificationEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status: "#/components/schemas/EventRoamingStatus" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country: "#/components/schemas/EventRoamingChangeCountry" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off: "#/components/schemas/EventRoamingOff" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on: "#/components/schemas/EventRoamingOn" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventRoamingStatus: + description: event structure for roaming status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingStatus" + + EventRoamingOn: + description: event structure for roaming on change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingOff: + description: event structure for roaming off change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingChangeCountry: + description: event structure for roaming change country + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingChangeCountry" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + RoamingStatus: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - roaming + properties: + roaming: + type: boolean + description: Roaming status. True, if it is roaming. + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + RoamingChangeCountry: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + - countryName + properties: + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + SubscriptionEnds: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + required: + - terminationReason + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ROAMING_STATUS: + value: + id: "123654" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + roaming: true + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-17T13:18:23.682Z" + + ROAMING_OFF: + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-18T13:18:23.682Z" + + ROAMING_ON: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + ROAMING_CHANGE_COUNTRY: + value: + id: "123657" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + countryCode: 214 + countryName: ["ES"] + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } +``` diff --git a/marked/DeviceStatus/code/API_definitions/device-roaming-status/raw.md b/marked/DeviceStatus/code/API_definitions/device-roaming-status/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4401cf628ea9dfdfe07c4a666174dec57638185e --- /dev/null +++ b/marked/DeviceStatus/code/API_definitions/device-roaming-status/raw.md @@ -0,0 +1,548 @@ +# device-roaming-status + +```yaml +openapi: 3.0.3 +info: + title: Device Roaming Status + description: | + This API provides the API consumer with the ability to query device roaming Status + + # Introduction + + ## Roaming Status + API consumer is able to verify whether a certain user device is in roaming situation (or not). + + The verification of the roaming situation depends on the network's ability. Additionally to the roaming status, when the device is in roaming situation, visited country information could be returned in the response. + + ## Possible Use-Cases + Roaming status verification could be useful in scenario such as (not exhaustive): + - For regulatory reasons, where a customer may need to be within a certain jurisdiction, or out with others, in order for transactions to be authorized + - For security / fraud reasons, to establish that a customer is located where they claim to be + - For service delivery reasons, to ensure that the customer has access to particular service, and will not incur roaming charges in accessing them + + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Roaming** : Roaming status - `true`, if device is in roaming situation - `false` else. + + * **Country** : Country code and name - visited country information, provided if the device is in roaming situation. + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ## Device roaming situation + + The endpoint `POST /retrieve` allows to get roaming status and country information (if device in roaming situation) synchronously. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the roaming status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined roaming status for the multi-SIM group as a whole, or + - return the roaming status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 1.0.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-roaming-status/v1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Roaming status retrieval + description: Operation to get device roaming status and country information (if roaming) synchronously +paths: + /retrieve: + post: + tags: + - Roaming status retrieval + summary: "Get the current roaming status and the country information" + description: Get the current roaming status and the country information + operationId: getRoamingStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusRequest" + required: true + responses: + "200": + description: Contains information about current roaming status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusResponse" + examples: + No-Country-Name: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 901 + countryName: [] + Single-Country-Code: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Multiple-Country-Codes: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 340 + countryName: ["BL", "GF", "GP", "MF", "MQ"] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + RoamingStatusResponse: + type: object + required: + - roaming + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + roaming: + $ref: "#/components/schemas/ActiveRoaming" + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + LastStatusTime: + description: Last time that the associated device roaming status was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ActiveRoaming: + description: Roaming status. True, if it is roaming + type: boolean + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + RoamingStatusRequest: + description: The request for retrieving the current roaming status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue +``` diff --git a/marked/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d17796265d0f0b80701e6143fb85fddeb341c2fe --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist/raw.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for connected-network-type 0.1.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type.yaml](/code/API_definitions/connected-network-type.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type.feature](/code/Test_definitions/connected-network-type.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7941985feae81e60a6b098d35f3c5e39fa55e476 --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for connected-network-type-subscriptions 0.1.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type-subscriptions.yaml](/code/API_definitions/connected-network-type-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type-subscriptions.feature](/code/Test_definitions/connected-network-type-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..48efe46000be381a58d0524da9c1cc91ccd9fa28 --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist/raw.md @@ -0,0 +1,24 @@ +# API Readiness Checklist + +Checklist for device-reachability-status 1.0.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-reachability-status.yaml](/code/API_definitions/device-reachability-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/device-reachability-status-User-Story.md](/documentation/API_documentation/device-reachability-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | [see issue #258](https://github.com/camaraproject/DeviceStatus/issues/258) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..758aff37e7ae4b095315df5d4d329f6d413a133c --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story/raw.md @@ -0,0 +1,20 @@ +# Device Reachability Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the reachability status of a user's device, so that I can determine whether the device is reachable via SMS, data (mobile internet), or both, enabling better communication or service management decisions based on real-time device availability. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                    **Scope:** Order To Activate (OTA) - Get connectivity status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the reachability status of a user's device | M | +| Ends when | The service provider returns the reachability status of the device with a timestamp when the status information was updated. In case of the device is reachable, additionally, the type of the connectivity (data, sms or both) is returned as well. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                    - Unauthorized: Invalid credentials (e.g., expired access token).
                    - Incorrect input data (e.g., malformed phone number).
                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) diff --git a/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..afbe8302bbae5e88a7453a712b8f1376eddbf976 --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for device-reachability-status-subscriptions 0.7.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-reachability-status-subscriptions.yaml](/code/API_definitions/device-reachability-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-reachability-status-subscriptions.feature](/code/Test_definitions/device-reachability-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..db31fcd77b97184d9aaea134c91eecaec34a7897 --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist/raw.md @@ -0,0 +1,24 @@ +# API Readiness Checklist + +Checklist for device-roaming-status 1.0.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-roaming-status.yaml](/code/API_definitions/device-roaming-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/device-roaming-status-User-Story.md](/documentation/API_documentation/device-roaming-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | [see issue #258](https://github.com/camaraproject/DeviceStatus/issues/258) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f3c0c1c784bcaafac2854b02da435e58b848f969 --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story/raw.md @@ -0,0 +1,21 @@ +# Device Roaming Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the roaming status of a user's device, so that I can determine whether a device is in a foreign network and in which country it is located. This API can be used to identify fraud, ensure regulatory compliance, or enforce territorial restrictions on video and audio content. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                    **Scope:** Order To Activate (OTA) - Get roaming status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the roaming status of a user's device | M | +| Ends when | The service provider returns the roaming status of the device with a timestamp when the status information was updated. In case of a roaming situation also the roaming country name and code shall be returned. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                    - Unauthorized: Invalid credentials (e.g., expired access token).
                    - Incorrect input data (e.g., malformed phone number).
                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) + diff --git a/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..853d62e4bafb80b3fc98144e9f5b61a4ab0a731f --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for device-roaming-status-subscriptions 0.7.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-roaming-status-subscriptions.yaml](/code/API_definitions/device-roaming-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-roaming-status-subscriptions.feature](/code/Test_definitions/device-roaming-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceStatus/documentation/API_documentation/resources/README/raw.md b/marked/DeviceStatus/documentation/API_documentation/resources/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceStatus/documentation/API_documentation/resources/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cb014a56be8ed6a708bea354d0206e4688404fad --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29/raw.md @@ -0,0 +1,48 @@ +# Camara DeviceStatus meeting - MOM-2023-03-29 + +*March 29th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Mona Mokhber (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Robert Ludivic (Orange) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + - rewrite the issue to one time request + - start discussion +* [#24 Tag version 0.2.0](https://github.com/camaraproject/DeviceStatus/issues/24) + - 0.2.0 release branch is created but it should be protected => this issue can be closed +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) + - related to the PR about subscriptions: https://github.com/camaraproject/WorkingGroups/pull/173 . This issue should be discussed or modified after its approval. +* [#15 Update commonalities glossary with subproject relevant terms](https://github.com/camaraproject/DeviceStatus/issues/15) + - update with camelcase names (Rafal) +* [#14 Align error message with structure defined in the guideline](https://github.com/camaraproject/DeviceStatus/issues/14) + - Mona creates the PR, target 0.5.0-wip + +### Open PRs +* [#33 Update MAINTAINERS.MD](https://github.com/camaraproject/DeviceStatus/pull/33) + - needs owner review +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + - on hold + +## AOB +* Create 0.4.0 release branch (Akos) +* Further releases should be developed as proposed in Commonalities, using -wip in the version name during development of the next release + +* Next call will be on 12.04.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7f60c600dbe24d20495add8580d2a8018ffb2774 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12/raw.md @@ -0,0 +1,47 @@ +# Camara DeviceStatus meeting - MOM-2023-04-12 + +*April 12th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Mona Mokhber (Telefonica) +* Murat Karabulut (Deutsche Telekom) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#37 Create release 0.4.0](https://github.com/camaraproject/DeviceStatus/issues/37) + - Eric will create the release +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + - start discussion +* [#24 Tag version 0.2.0](https://github.com/camaraproject/DeviceStatus/issues/24) + - 0.2.0 release branch is created but it should be protected => this issue can be closed + - codeowners have no rights for branch protection (Akos will contact Herbert about it) +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) + - related to the PR about subscriptions: https://github.com/camaraproject/WorkingGroups/pull/173 . This issue should be discussed or modified after its approval. +* [#14 Align error message with structure defined in the guideline](https://github.com/camaraproject/DeviceStatus/issues/14) + +### Open PRs +* [#35 Errors definition alignment with guidelines](https://github.com/camaraproject/DeviceStatus/pull/35) + - additional approvals required +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + - on hold + +## AOB +* Next call will be on 26.04.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b7fba646612ca3e770810d05fd4f2d934db3bd58 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21/raw.md @@ -0,0 +1,44 @@ +# Camara DeviceStatus meeting - MOM-2023-06-21 + +*June 21st, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Will be fixed in [PR31](https://github.com/camaraproject/DeviceStatus/pull/31) + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +Open issue: which type of connectivity is needed. +Input from Jorge: GSMA is already working on the use cases, which possible should be considered in CAMARA also. Decision: we wait until next DeviceStatus call. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is open + +### Open PRs +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + + +## AOB +* Create API roadmap draft => Akos +* Create Issue for documentation => Akos + +* Next call will be on 05.07.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b7f65105ea05dd5c08dd10cd9d2811d6adcff09e --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05/raw.md @@ -0,0 +1,56 @@ +# Camara DeviceStatus meeting - MOM-2023-07-05 + +*July 5th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Mona Mokhber (Telefonica) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Will be fixed in [PR31](https://github.com/camaraproject/DeviceStatus/pull/31) + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +No input from GSMA available. The PR can be created, based on the discussions. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is open + +## Open PRs +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + +## API Roadmap +### Release 0.5.0 +* July-August 2023 +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) / +[PR#31](https://github.com/camaraproject/DeviceStatus/pull/31) + +### Release 0.6.0 +* September-Oktober 2023 +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + +## AOB + +* Next call will be on 19.07.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..45562413ccd2fe01f316d5fa79326e8673167e54 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19/raw.md @@ -0,0 +1,64 @@ +# Camara DeviceStatus meeting - MOM-2023-07-19 + +*July 19th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Masaharu Hattori (KDDI) +* Mona Mokhber (Telefonica) +* Rafal Artych (Deutsche Telekom) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR65](https://github.com/camaraproject/DeviceStatus/pull/65) is open. + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Has been fixed by [PR31](https://github.com/camaraproject/DeviceStatus/pull/31), the issue can be closed. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +No input from GSMA available. The PR can be created, based on the discussions. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is closed, the issue can be closed too. + +## Open PRs +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + The goal is to merge the PR by the end of CW29. + +## API Roadmap +### Release 0.5.0 +* July-August 2023 +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* After [PR#65](https://github.com/camaraproject/DeviceStatus/pull/65) has been merged, the release can be created (Eric). + +### Release 0.6.0 +* September-Oktober 2023 +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + +## AOB + +* New issue: How to handle mandatory and optional features of each API + * Definition of minimum implementation of a Camara API + * How can a provider inform the ASP/aggregator about not implemented features in advance of the API call? + * An issue in commonalities should be created +* Next call will be on 02.08.2023 11:00 CET + diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7af8acfc0eb81832a52775f394595b853e5a5678 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13/raw.md @@ -0,0 +1,72 @@ + # Camara DeviceStatus meeting - MOM-2023-09-13 + +*September 13th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Prashant Sidana (E&) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR65](https://github.com/camaraproject/DeviceStatus/pull/65) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) + +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + The PR should be adapted when CloudEvents will be introduced => status delayed. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of the planned switch to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + + +## AOB + +* New issue: How to handle mandatory and optional features of each API + * Definition of minimum implementation of a Camara API + * How can a provider inform the ASP/aggregator about not implemented features in advance of the API call? + * An issue in commonalities should be created (Prashant) +* New issue: Change notifications to be based on CloudEvents + The issue is linked to the related issues/PRs in Commonalities (add links). + The issue should also add missing event types for connectivity status. (after [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) has been merged.) + +* Next call will be on 27.09.2023 11:00 CET + diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a42761942ceb36ca88b75216685d128d0b2f0d77 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27/raw.md @@ -0,0 +1,70 @@ + # Camara DeviceStatus meeting - MOM-2023-09-27 + +*September 27th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. This issue can be closed. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Based on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of switching to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 11.10.2023 11:00 CET + diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9fce1782c4bca593dde9cfb65dc125f388d63927 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11/raw.md @@ -0,0 +1,71 @@ +# Camara DeviceStatus meeting - MOM-2023-10-11 + +*October 11th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Noel Wirzius (Deutsche Telekom) +* Prashant Sidana (E&) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. This issue can be closed. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Depending on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) +Reviews are requested. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of switching to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 25.10.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..168cb500a0bf65384dbd0239bfb69c713e549161 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25/raw.md @@ -0,0 +1,65 @@ +# Camara DeviceStatus meeting - MOM-2023-10-25 + +*October 25th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Depending on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) +Reviews are requested. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* After merging all PRs the first Releasecandidate should be created +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 08.11.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1519f983a343046cdb63f670f0e3fe3f77ec0275 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08/raw.md @@ -0,0 +1,54 @@ +# Camara DeviceStatus meeting - MOM-2023-11-08 + +*November 8th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) +* Sebastian Köller (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) extends the API with connectivity related events. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Status: open for reviews. + +## API Roadmap + +### Release 0.5.0 +* November 2023 +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) +* [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) +* After merging all PRs the first Releasecandidate should be created +### Release 0.6.0 +* Q1 2024 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 22.11.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bc41d2f51dbd5c592e5965051ab3ed11cc3f044b --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22/raw.md @@ -0,0 +1,51 @@ +# Camara DeviceStatus meeting - MOM-2023-11-22 + +*November 22nd, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) + A PR should be created. + +* [#81 enhance v0.4.1 to follow latest CAMARA guidelines](https://github.com/camaraproject/DeviceStatus/issues/81) + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +Almost all requirements have been implemented (except support for multiple devices), the issue should be closed. + + +## Open PRs +* + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the planned release content has been merged, the first release candidate should be created. +* Release content: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) + +## AOB +* Next call will be on 06.12.2023 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a59b9d488349f0b162bfa84c8d1c1a9994f2598f --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06/raw.md @@ -0,0 +1,58 @@ +# Camara DeviceStatus meeting - MOM-2023-12-06 + +*December 6th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* Open Discussions +* API Roadmap +* AOB + + +## Open issues: +* [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + We agreed, that the issue can be implemented as proposed. + +* [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) +PR is open. + +* [#81 enhance v0.4.1 to follow latest CAMARA guidelines](https://github.com/camaraproject/DeviceStatus/issues/81) + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +Almost all requirements have been implemented (except support for multiple devices), the issue should be closed. + +## Open PRs +* [#87 Create release candidate 0.5.0-rc](https://github.com/camaraproject/DeviceStatus/pull/87) +The PR is blocked by [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + +## Open discussions +* + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the planned release content has been merged, the first release candidate should be created. +* Release content: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + * [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) => [PR#87](https://github.com/camaraproject/DeviceStatus/pull/87) + +## AOB +* Next call will be on 20.12.2023 11:00 CET - However, when the 0.5.0-rc could be created earlier then this call should be skipped. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..23e1d3de11c0fe1fe333f9a3fff5b7b90a35e1ba --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17/raw.md @@ -0,0 +1,67 @@ +# Camara DeviceStatus meeting - MOM-2024-01-17 + +*January 17th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* Open Discussions +* API Roadmap +* AOB + + +## Open issues: +* [#97 Update response codes to string, following other CAMARA APIs](https://github.com/camaraproject/DeviceStatus/issues/97) + The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) +The issue should be implemented after releasing the 0.5.0. + +* [#94 Corrections needed to resolve linting errors](https://github.com/camaraproject/DeviceStatus/issues/94) + The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +## Open PRs +* [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + The PR is ready to be merged. + +## Open discussions +* [#98 Roaming Status - AgeOfInformation (or last_updated_timestamp)](https://github.com/camaraproject/DeviceStatus/discussions/98) + It should be converted to an issue to continue the discussion there. +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the release candidate 0.5.0-rc has been created. If no more bugs or findings in the 0.5.0-rc will be reported in the next 2 weeks, then the official release 0.5.0 can be created (no rc2 is necessary). +* Release content 0.5.0-rc: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [~~#84 Minor corrections in Subscription model before release~~](https://github.com/camaraproject/DeviceStatus/issues/84) + * [~~#82 Create release candidate 0.5.0~~](https://github.com/camaraproject/DeviceStatus/issues/82) => [PR#87](https://github.com/camaraproject/DeviceStatus/pull/87) +* Release content 0.5.0: + * [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + * New issue&PR to prepare the release + +## AOB +* Next call will be on 14.02.2024 11:00 CET +* Since the API is already in a mature status, a v1.0.0 should be targeted. => Create an issue to discuss about the process and the necessary to-do's. +* An issue for creation of the necessary feature file for testing should be created too. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..830c6cec9e7d9c9a878b2db516937154ad3a2de1 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14/raw.md @@ -0,0 +1,82 @@ +# Camara DeviceStatus meeting - MOM-2024-02-14 + +*February 14th, 2024* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * Renaming the POST endpoints according to the design guidelines. No discussion, can be merged after approvals. + +* [#109 fix: add missing "subscriptionId" in "RoamingStatus"-data for CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/109) + * No discussion, can be merged after approvals. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + +## Open issues: + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + * Is the information on 3GPP available at all? + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * No discussion, a PR should be created. + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#97 Update response codes to string, following other CAMARA APIs](https://github.com/camaraproject/DeviceStatus/issues/97) + * The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* [#105 v0.5.0 - Difference between "subscriptionExpireTime" & "expiresAt" in "SubscriptionInfo"](https://github.com/camaraproject/DeviceStatus/discussions/105) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#98 Roaming Status - AgeOfInformation (or last_updated_timestamp)](https://github.com/camaraproject/DeviceStatus/discussions/98) + * An issue [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) has been created, the discussion can be closed. +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Status: release created on 31.01.2024 + +### Release 0.6.0 +* Planned release date: tbd +* Status: wip +* Content: + + +## AOB +* Next call will be on 28.02.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created too. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17d7db55aa2a664986d77fb227338f75807093e5 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28/raw.md @@ -0,0 +1,88 @@ +# Camara DeviceStatus meeting - MOM-2024-02-28 + +*February 28th, 2024* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * Renaming the POST endpoints according to the design guidelines. + * No discussion, can be merged after approvals. + +* [#109 fix: add missing "subscriptionId" in "RoamingStatus"-data for CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/109) + * No discussion, can be merged after approvals. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + +## Open issues: + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * Same issue exists in Device Location + * Should be addressed in Commonalities + +* [#116 subscriptionExpireTime is declared as "required" in the subscription-ends - note, but is optional currently](https://github.com/camaraproject/DeviceStatus/issues/116) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* **[#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114)** +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Status: release created on 31.01.2024 + +### Release 0.6.0 +* Planned release date: tbd +* Status: wip +* Content: A proposal for the content should be created (Ákos) + + +## AOB +* Next call will be on 13.03.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..54e5bfdd3dcccff1376ab0ffbcbcf8a997541475 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13/raw.md @@ -0,0 +1,112 @@ +# Camara DeviceStatus meeting - MOM-2024-03-13 + +*March 13th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Ludovic Robert (Orange) +* Maximilian Laue (Deutsche Telekom) +* Quanain Meghjee (Vonage) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) +* Toyeeb Rehmann (GSMA) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs + +* [#127 Updated in-line documentation for Roaming to clarify that country information can optionally be returned in the response](https://github.com/camaraproject/DeviceStatus/pull/127) + +* [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * No discussion + * Reviews are missing. + +* [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + * Should be first clarified in Commonalities: camaraproject/Commonalities#153 + +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + * The fix for the typo should be covered in a separate PR. + +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * The PR has been merged accidentally, but then the change has been reverted. This PR should be merged after the bugfix release v0.5.1 has been created. + * A new PR should be opened. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + * An issue in Commonalities has been opened camaraproject/DeviceLocation#149 + +## Open issues: + +* [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + * Split the current API into 4 different APIs + +* [#124 When roaming status is true, is it mandatory to return both countryCode and countryName?](https://github.com/camaraproject/DeviceStatus/issues/124) + +* [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +* [#119 How can a provider inform the ASP/aggregator about not implemented features in advance of the API call](https://github.com/camaraproject/DeviceStatus/issues/119) + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * The corresponding PR is open: [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * A new PR should be created see [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* [#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.x +* The release v0.5.0 was created on 31.01.2024 +* The bugfix release 0.5.1 is planned [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +### Release 0.6.0 +* Planned release date: tbd +* Content: + * [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * ?? [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + + +## AOB +* Next call will be on 27.03.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created. diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7dc58049f62c4484256969748616baed58fc4235 --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27/raw.md @@ -0,0 +1,117 @@ +# Camara DeviceStatus meeting - MOM-2024-03-27 + +*March 27th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Ankita () +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Quanain Meghjee (Vonage) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs + +* [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + * PR was recreated after accedentally merging too early + * Planned release v0.6.0 + +* [#129 fix: change INVALID_INPUT for INVALID_ARGUMENT according to guidelines](https://github.com/camaraproject/DeviceStatus/pull/129) + * Review in progress + * Planned release v0.5.1 + +* [#127 Updated in-line documentation for Roaming to clarify that country information can optionally be returned in the response](https://github.com/camaraproject/DeviceStatus/pull/127) + * Review in progress + * Planned release v0.5.1 + +* [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * No discussion + * Reviews are missing. + +* [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + * Should be first clarified in Commonalities: camaraproject/Commonalities#153 + +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + * Planned release v0.6.0 + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + * An issue in Commonalities has been opened camaraproject/DeviceLocation#149 + +## Open issues: + +* [#130 What should the API return if more than one device identifier is sent and they don't belong to the same device?](https://github.com/camaraproject/DeviceStatus/pull/130) + +* [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + * Split the current API into 4 different APIs + +* [#124 When roaming status is true, is it mandatory to return both countryCode and countryName?](https://github.com/camaraproject/DeviceStatus/issues/124) + +* [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +* [#119 How can a provider inform the ASP/aggregator about not implemented features in advance of the API call](https://github.com/camaraproject/DeviceStatus/issues/119) + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * The corresponding PR is open: [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + + + +## Open discussions +* [#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.x +* The release v0.5.0 was created on 31.01.2024 +* The bugfix release 0.5.1 is planned [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +### Release 0.6.0 +* Planned release date: tbd +* Content: + * [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + * [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * ?? [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + + +## AOB +* Next call will be on 10.04.2024 11:00 CET diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..292abcb6cb43294991d033fcce65c7257d4a4a8c --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12/raw.md @@ -0,0 +1,35 @@ +# Meeting Minutes: Device Status WG +## Date: 12th December 2022 +## Attendees +- Eric Murray / Vodafone +- Sachin Kumar / Vodafone +- Ludovic Robert / Orange +- Joachim Dahlgren / Ericsson +- Mona Mokhber / Telefonica +## Pull Requests +- PR #8: Add documentation / DT + + It was agreed that: + - Final reviews of this PR should be undertaken this week + - Any comments to be raised by end of Friday 16th December, otherwise it will be approved +- PR #9: v0.3.0 based on Telefónica proposal / Telefonica + + It was agreed that: + - Outstanding issues / PRs in the Commonalities WG ([PR #68](https://github.com/camaraproject/WorkingGroups/pull/68), [Issue #101](https://github.com/camaraproject/WorkingGroups/issues/101), [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105)) need to be closed before this proposal can be progressed + - A separate API per status type (in this case, roaming status) was the best approach, and new APIs should be introduced for additional statuses (e.g. device connectivity state) + - If additional roaming status information was to be added (e.g. visited country, or PLMN ID), this should be implemented as additional paths to support different client access rights via scopes +## Issues +- Issue #6: Issues, branches, pull requests - cleaning up + - Issue closed +- Issue #7: Meetings ? + - Agreed to keep open until Noel has scheduled ongoing bi-weekly meetings +- Issue #2: Roaming Status API Proposal + - This was the original issue raised in the Commonalities WG, and now transferred to Device Status WG + - Agreed to revisit once PR #9 is resolved + - Link to original proposal is broken. Eric to copy over original proposal to Device Status WG and fix link. +- Issue #10: Telefonica proposal post MWC + - Issue raised to introduce PR #9 (discussed above). Can be used to raise questions about the proposal. +## Discussions +- None +## AOB +- Ongoing meetings to be scheduled by Noel. Anyone wishing to join should subscribe to the [mailing list](https://lists.camaraproject.org/g/sp-dst). diff --git a/marked/DeviceStatus/documentation/MeetingMinutes/README/raw.md b/marked/DeviceStatus/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceStatus/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceStatus/documentation/SupportingDocuments/README/raw.md b/marked/DeviceStatus/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceStatus/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone/raw.md b/marked/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a554ea03c63cbd4153d4cc64229aacd9adfde012 --- /dev/null +++ b/marked/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone/raw.md @@ -0,0 +1,31 @@ +# Roaming Status API +Device (i.e. UE) status indications are an important family of APIs where the API consumer is not the device itself. One status indication that has several use cases is the roaming status of the device. Roaming in this context is defined as being connected to a network other than the subscriber's home network, and so would include national roaming (where allowed) in addition to international roaming. + +For example, such information could be useful in the following scenarios: +- For regulatory reasons, where a customer may need to be within a certain jurisdication, or outwith others, in order for transactions to be authorised +- For security / fraud reasons, to establish that a customer is located where they claim to be +- For service delivery reasons, to ensure that the customer has access to particular services, and will not incur roaming charges in accessing them + +### Inputs +- The target UE whose roaming status is required should be explicitly identified by its GPSI (MSISDN or External Identifier). It is not expected that the UE itself will call this API, and hence OIDC will not identify the target UE. +- When a boolean indication of whether or not a UE is in a specific country, the ISO country code for that country must be provided + + +### Outputs +It is proposed that a roaming status API is able to provide the following information to API consumers: +- A boolean indicator of roaming state (i.e. roaming / not roaming) +- if roaming, an indicator of whether that is national or international roaming (i.e. does the ISO country code for the home MCC equal that of the visited MCC or not) +- The ISO country code corresponding to the MCC of the network the device is currently connected to or, where the MCC does not have a corresponding ISO country code, the MCC itself +- The full PLMN of the network that the device is currently connected to (MCC + MNC) +- A boolean indicator of whether a device is in a specified country (specified by ISO country code) + +### Notifications +It should be possible for the API caller to be notified of any change in roaming status + +## Implementation +UE roaming status information can be obtained either directly from the HSS, or via the SCEF/NEF "ROAMING_STATUS" monitoring capability + +## Notes +- API consumers would be able to access all or only some of this information, depending on their level of authorisation +- Some lucky countries (e.g. UK, USA, India, China) have multiple MCCs, hence care must be taken when deciding roaming status on the basis of the visited network MCC +- A very few MCCs are shared between multiple countries (specifically, countries with different ISO country codes - for example, French DROMs or British Crown Dependencies). In these cases, the ISO country code needs to be determined from the full visited network PLMN. diff --git a/marked/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis/raw.md b/marked/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..87bc364f1931f591185a692c8e1eeb2cd0d83687 --- /dev/null +++ b/marked/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis/raw.md @@ -0,0 +1,136 @@ +# Decision supporting document for the discussion 1 or 2(n) APIs + +## Current situation +The device-status API has 1 endpoint: /roaming. +There is a need to add new functionalities. At first 2 new endpoints: to get the connectivity status and to subscribe for status-events. +Later other functionalities will follow. + +### Option 1 +Logically related endpoints are generally within 1 API, with 1 basepath. In special cases (e.g. compliance) splitting is possible. +Example: +{apiRoot}/device-status/v0/roaming +{apiRoot}/device-status/v0/connectivity +{apiRoot}/device-status/v0/subscriptions + +### Option 2 +Each device status subtype is handled in a separate API with different basepaths building an API-family. +Example: +API #1 +{apiRoot}/device-roaming-status/v0/roaming +{apiRoot}/device-roaming-status/v0/subscriptions + +API #2 +{apiRoot}/device-connectivity-status/v0/connectivity +{apiRoot}/device-connectivity-status/v0/subscriptions + + +## Criterias + +### 1. API usage - client view + +Aspects of finding and using the API(s) for a specific use case of a client. + +**Separate basepath** + +Pros: +- For a use case with a single area of interest (e.g. only roaming status is needed) a specific small API might be easier to be found and used + +Cons: +- For more complex use cases many device status-APIs are needed (find, subscribe, integrate, etc.) + + +**Common basepath** + +Pros: +- For a use case with multiple areas of interest or the intention to extend the usage later a combined API with all device status related information is more comfortable +- Only one API onboarding +- In this very specific context, the 2 functions are very close. + +Cons: +- If only one specific status is needed, then it might take longer to find the right information + + +### 2. Service development and operation - provider view +Aspects of the service implementation, testing, and operation on the provider side. + +**Separate basepath** + +Pros: +- Independent implementation and testing of the different status functionalities +- Fine-grade billing, scaling and monitoring is possible (however more effort) + +Cons: +- Extra effort is needed to prevent doubled code +- More overhead on developing and operating multiple services + +**Common basepath** + +Pros: +- Efficient development (especially when all status information can be gathered from the same southbound service) +- Model generation performed once + +Cons: +- If different southbound services are used the service gets more complex +- It might lead to partial implementations when there is an interest in some of the use cases and not the others + + +### 3. API maintenance & releasing - Camara view +Aspects of maintenance (add, delete, change functionality) and releasing (versioning, release planning, etc.) + +**Separate basepath** + +Pros: +- A simple service is easier to maintain and release +- Version changes are tightly related to the API functionality + +Cons: +- The overall effort (discussions, YAML work, etc.) for the API family is higher +- Additional synchronization within the API family is necessary (using common types could help) + +**Common basepath** + +Pros: +- Bigger releases with higher value +- Easy to add a new endpoint to an existing API + +Cons: +- Longer release cycles (more content, more discussions) +- Introducing changes/updates in one of the endpoints will result a version change affecting other unrelated endpoints (specially when they are not backward compatible) + + +### 4. Harmonization - technical view +Aspects of industry best practice, generic design guidelines and harmonization with other Camara APIs. + +**Some examples** +- 3GPP APIs are simple on the path level (collection and collection\\), inside the requests/responses many subtypes are used +- TM-Forum APIs contain multiple different endpoints related to the API theme +- Camara APIs don't show a clear picture (range from very simple to "monster" APIs) + +**Separate basepath** + +Pros: +- Small API and microservice with very limited responsibility (however 1 microservice can implement multiple APIs also) + +Cons: +- Atomic APIs with very limited scopes are not typical + +**Common basepath** + +Pros: +- + +Cons: +- + +## Preference + +| Company | Preference | +| ------- | ---------- | +| Orange | Slight preference for one API with 2 resources but not a 'structral' point for us for this API. | +| Vodafone | Based on the information shared at https://github.com/camaraproject/WorkingGroups/discussions/218 against different other aspects, our preference is to have separate APIs for each status (Roaming/Connectivity). | +| Deutsche Telekom | We prefer the solution with a common basepath (1 API), however in specific cases a separation is conceivable | +| Telfónica | Our preference is to have separate APIs for different types of status | + + + + diff --git a/marked/DeviceSwap/README/raw.md b/marked/DeviceSwap/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d27c016466cb5f3be35842ef2fa25071a3498354 --- /dev/null +++ b/marked/DeviceSwap/README/raw.md @@ -0,0 +1,54 @@ + + + + + + + + + +# DeviceSwap + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceSwap Service API(s) within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ijLe) + +## Scope +* Service APIs for “Device Swap” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * understand if the MSISDN has had a change of device in the last 30 days. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2024 +* * Incubating stage since: June 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/DeviceSwap/releases/tag/r3.2) (Fall25), with the following API versions: + * **device-swap v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceSwap/blob/r3.2/code/API_definitions/device-swap.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceSwap/r3.2/code/API_definitions/device-swap.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceSwap/r3.2/code/API_definitions/device-swap.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceSwap/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceSwap/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceSwap/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Every 4 weeks Thursday at 7:30 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/hDze) + * [Minutes archive](https://lf-camaraproject.atlassian.net/wiki/x/5VPe) before May 2025 + +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceSwap/code/API_definitions/device-swap/raw.md b/marked/DeviceSwap/code/API_definitions/device-swap/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7fb223b33a685fae0fe375c896c46cb5e553e8dc --- /dev/null +++ b/marked/DeviceSwap/code/API_definitions/device-swap/raw.md @@ -0,0 +1,516 @@ +# device-swap + +```yaml +openapi: 3.0.3 +info: + title: Device Swap + description: | + This API allows to check the last time that the phone (device) - phone number association has changed + + # Introduction + + The Device Swap API performs real-time checks on the last Device Swap event, providing real-time information about whether the SIM card associated with a user's phone number has been transferred to a different physical device. + + Device Swap information can be invaluable for enhancing security, fraud detection, and ensuring compliance with regulatory requirements in various applications, apart from providing useful information of device upgrade trends in user segments. + + This API is used by an application to get information about a mobile line's latest Device Swap date. It can be easily integrated and used through this secured API and allows API consumers to get this information in an easy and secured way. The API provides management of 2 endpoints answering 2 distinct questions: + + * When did the last Device Swap occur? + * Has a Device Swap occurred during the last n hours? + + # Relevant terms and definitions + + **Device Swap:** A Device Swap is a process in which the association between a user's mobile phone number (MSISDN) and a device (IMEI) is created for the first time or changes for any reasons. + + # API Functionality + + The Device Swap API provides a programmable interface for developers and other users (capabilities consumers) to request the last date of a device swap performed on the mobile line, or, to check whether a device swap has been performed during a past period. + + The API provides 2 operations: + + - POST retrieve-date: Provides timestamp of latest device swap, if any, for a given phone number. + - If no swap has been performed and the network operator supports unlimited DeviceSwap monitoring timeframe, the API will return the first phone number usage in a device (the timestamp of the first time that the phone number was connected to the network, it is, the first time that the SIM is installed in a device). + - If the latest device swap date (or the first phone number usage, if no device swap) cannot be communicated due to local regulations (or Network Operator internal privacy policies) preventing the safekeeping of the information for longer than the stated period, a `null` value will be returned. Optionally, a `monitoredPeriod` could be provided to indicate monitored time frame (in days) supported by the Network Operator. In this case the response must be treated as "there were no device swap events during 'monitoredPeriod'. Either the parameter is optional, it is recommended to support it in DeviceSwap implementations. + - POST check: Checks if device swap has been performed during a past period (defined in the request with 'maxAge' attribute) for a given phone number, the API will return boolean response (true/false), indicating that the device has been swapped or not in the specified period. In case the phone number has never been installed in a device, or no data is available in the operators records (e.g. database error), API will return a 422 error. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API. There is 2 ways to retrieve it depending on the authorization flow used: + - When the API is invoked using a two-legged access token, the phone number will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the phone number will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the phoneNumber cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the phoneNumber can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceSwap + +servers: + - url: '{apiRoot}/device-swap/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Retrieve Device Swap Date + description: Receive the last date in which the device of the end-user was swapped + - name: Check Device Swap + description: Validate if the SIM of the end-user has been installed in a different device during a past period +paths: + /retrieve-date: + post: + tags: + - Retrieve Device Swap Date + summary: Get last device swap date + description: Get timestamp of last device swap for a mobile user account provided with phone number. + operationId: retrieveDeviceSwapDate + security: + - openId: + - device-swap + - openId: + - device-swap:retrieve-date + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a device swap date request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateDeviceSwapDate" + examples: + RETRIEVE_3LEGS: + $ref: "#/components/examples/RETRIEVE_3LEGS" + RETRIEVE_2LEGS: + $ref: "#/components/examples/RETRIEVE_2LEGS" + required: true + responses: + "200": + description: Contains information about Device swap change + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceSwapInfo" + examples: + RETRIEVE_DATE: + $ref: "#/components/examples/RETRIEVE_DATE" + RETRIEVE_MONITORED_PERIOD: + $ref: "#/components/examples/RETRIEVE_MONITORED_PERIOD" + RETRIEVE_MONITORED_NULL: + $ref: "#/components/examples/RETRIEVE_MONITORED_NULL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + /check: + post: + tags: + - Check Device Swap + summary: Check last device swap date + description: Check if device swap has been performed during a past period + operationId: checkDeviceSwap + security: + - openId: + - device-swap + - openId: + - device-swap:check + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + description: | + Create a check device swap request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateCheckDeviceSwap" + examples: + CHECK_3LEGS: + $ref: "#/components/examples/CHECK_3LEGS" + CHECK_2LEGS: + $ref: "#/components/examples/CHECK_2LEGS" + responses: + "200": + description: Returns whether a device swap has been performed during a past period + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDeviceSwapInfo" + "400": + $ref: "#/components/responses/Generic400Check" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + DeviceSwapInfo: + type: object + required: + - latestDeviceChange + properties: + latestDeviceChange: + type: string + format: date-time + description: Timestamp of latest device swap performed. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + monitoredPeriod: + type: integer + description: Timeframe in days for device change supervision for the phone number. It could be valued in the response if the latest Device swap occurred before this monitored period. + example: 120 + CreateDeviceSwapDate: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + CreateCheckDeviceSwap: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + maxAge: + type: integer + example: 240 + description: | + Period in hours to be checked for device swap. + format: int32 + minimum: 1 + maximum: 2400 + default: 240 + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+34666111333' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + CheckDeviceSwapInfo: + type: object + required: + - swapped + properties: + swapped: + type: boolean + description: Indicates whether the device has been swapped during the period within the provided age. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic400Check: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: phone number is not included in the request (in case of 2-legged) or the phone number identification cannot be derived from access token (in 3-legged) + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. + examples: + RETRIEVE_DATE: + summary: Lastest Device swap date is send back + value: + latestDeviceChange: 2024-09-18T07:37:53.471829447Z + RETRIEVE_MONITORED_NULL: + summary: Only null value is retrieved + value: + latestDeviceChange: null + RETRIEVE_MONITORED_PERIOD: + summary: null is send back for the date but a monitoredPeriod is provided + value: + latestDeviceChange: null + monitoredPeriod: 120 + CHECK_2LEGS: + summary: Check request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + maxAge: 120 + CHECK_3LEGS: + summary: Check request with 3-legged access tokens + value: + maxAge: 120 + RETRIEVE_2LEGS: + summary: Retrieve request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + RETRIEVE_3LEGS: + summary: Retrieve request with 3-legged access tokens + value: + {} +``` diff --git a/marked/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist/raw.md b/marked/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cd6daada4d8326d83edbe1faf8eb3a8c7c38c0b3 --- /dev/null +++ b/marked/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist/raw.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for device-swap v1.0.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                    public | stable
                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](code/API_definitions/device-swap.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v1.0.0 | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/device-swap.yaml) | +| 6 | User stories | O | O | O | M | Y | [check](/documentation/API_documentation/device-swap_check_User_Story.md) [retrieve](/documentation/API_documentation/device-swap_retrieve_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [check](/code/Test_definitions/device-swap-checkDeviceSwap.feature) [retrieve](/code/Test_definitions/device-swap-retrieveDeviceSwapDate.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [check](/code/Test_definitions/device-swap-checkDeviceSwap.feature) [retrieve](/code/Test_definitions/device-swap-retrieveDeviceSwapDate.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue [#68](https://github.com/camaraproject/DeviceSwap/issues/68) | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166764/DeviceSwap+API+description) | + +(*) If you encounter issues with the provided test files (.feature), please create an issue in the API Sub-Project to signal these issues so they can be fixed in a patch release. + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story/raw.md b/marked/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f12e722d015d84f933b41a5a56dc1ee4891f8483 --- /dev/null +++ b/marked/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story/raw.md @@ -0,0 +1,11 @@ +# Device Swap Check API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check if a device swap has occurred within a specified period for a user's mobile number so that I can enhance security measures against account takeover fraud. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                    **Scope:**
                    - Checks if a device swap has occurred within a specified period for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:

                    1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                    2. The ASP:BusinessManager has successfully subscribed to the Device Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                    3. The ASP:Administrator has onboarded the ASP:User to the platform.
                    4. The ASP:User performs an authorization request to CSP
                    5. The CSP checks access & End-User approval then provide access token to the ASP:User
                    6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Device Swap API, providing the phone number and the desired period to check for device swaps. This request could be done via (or not) the Channel Partner.
                      **Ends when:** The CSP's Device Swap server responds indicating whether a Device Swap has been performed within the specified period. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the End-User's line, based on the Device Swap information. | +| ***Exceptions*** | Several exceptions might occur during the Device Swap API operations
                      - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                      - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| diff --git a/marked/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story/raw.md b/marked/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a18bf4803581da30f88b9947dec79aa720347ab9 --- /dev/null +++ b/marked/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story/raw.md @@ -0,0 +1,11 @@ +# Device Swap Retrieve API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the last device swap date for a user's mobile number so that I can enhance security measures against account takeover fraud. | +|***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                      **Scope:**
                      - Retrieves the timestamp of the last device swap event for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                      1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                      2. The ASP:BusinessManager has successfully subscribed to the Device Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                      3. The ASP:Administrator has onboarded the ASP:User to the platform.
                      4. The ASP:User performs an authorization request to CSP
                      5. The CSP checks access & End-User approval then provide access token to the ASP:User
                      6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Device Swap API, including the phone number provided by the End-User in the ASP:User.
                        **Ends when:** The CSP's Device Swap server responds with the timestamp of the last device swap event, or the first SIM installation date if no device swap has occurred. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the End-User's line, based on the Device Swap information. | +| ***Exceptions*** | Several exceptions might occur during the Device Swap API operations
                        - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                        - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).
                        - Not able to provide: Legal restrictions or data retention policies preventing the retrieval of the requested information.| diff --git a/marked/DeviceSwap/documentation/MeetingMinutes/README/raw.md b/marked/DeviceSwap/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceSwap/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceSwap/documentation/SupportingDocuments/README/raw.md b/marked/DeviceSwap/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceSwap/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceVisitLocation/README/raw.md b/marked/DeviceVisitLocation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aaa3adb3a315d888a9c0bf9615b9b1272e6558b9 --- /dev/null +++ b/marked/DeviceVisitLocation/README/raw.md @@ -0,0 +1,41 @@ + + + + + + + + + +# DeviceVisitLocation + +Sandbox API Repository to describe, develop, document, and test the DeviceVisitLocation Service API(s), working closely together with MostFrequentLocation. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQCICQ) + +## Scope + +* Service API(s) “DeviceVisitLocation” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * query the visit locations of a device during a certain time period. +* Describe, develop, document, and test the API(s) +* Started: May 2024 (originally as part of LocationInsights, own repository since July 2025) + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly, Thursday, 09:00 CEST (07:00 UTC) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99479758031?password=c705dd6f-a1c5-44e4-af97-331a18395fb8) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/XjPe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/DeviceVisitLocation/code/API_definitions/device-visit-location/raw.md b/marked/DeviceVisitLocation/code/API_definitions/device-visit-location/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6c2f7fb4d089a266486cfa9f4a84ba6c80c50f64 --- /dev/null +++ b/marked/DeviceVisitLocation/code/API_definitions/device-visit-location/raw.md @@ -0,0 +1,776 @@ +# device-visit-location + +```yaml +--- +openapi: 3.0.3 +info: + title: Device Visit Location + description: > + The Device Visit Location API provides customers with the ability + to query the visit locations of a device during a certain time period. + + # Introduction + + This API can return the visited location of a device at a certain time, and the visited location is returned as a list of geoCode objects. + + This API can be used in the following scenarios.\ + + **Anti fraud**: for some scenarios involving high-risk financial operations (such as cross-border transfers, large investments, etc.), by monitoring changes in the location visited by mobile phone numbers, potential fraudulent behavior can be detected in advance. For example, when a user usually only operates in a few provinces within the country, but suddenly has access records from overseas or unfamiliar high-risk provinces, and there are also signs of abnormal fund flow, preventive measures can be taken quickly.\ + + **Identity verification**: In the financial field, when users perform high-risk operations such as large transfers or changing important account information, in addition to conventional verification methods such as passwords and verification codes, identity verification can also be carried out by combining their phone number with the province they recently visited.\ + + **Remote abnormal operation detection**: For the account security management of e-commerce platforms, when users perform login, password modification, payment and other operations, they can use this api to detect whether there are abnormal operations in remote locations. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + * **geoCode**: An object with the following attributes: + - **countryCode**: The code of the country.Following the `ISO 3166 ALPHA-2` standard. + - **codeType**: The type of code, such as "PostlCode". + - **codeValue**: The actual value of the code. + # API Functionality + + Once the API Consumer provides the device infomation and specifies the time window, the API queries the relevant data. The data is retrieved from the stored information within the selected time window. The result is returned as a list of geoCode objects representing the visited locations. + + ## Detailed Explanation of GeoCode Object + + **CountyCode**: This is a string type field used to specify the country code where the location is located. Following the `ISO 3166 ALPHA-2` standard, for example, "CN" represents China, "US" represents the United States, etc. On a global scale, this code ensures accurate differentiation of different countries and is an important foundational information for positioning, helping to quickly filter and identify location data for specific countries in cross-border business or data analysis.\ + + **codeType**: String type, used to specify the geographic encoding type used, with a fixed value of `PostlCode` in the current version. This field is designed to facilitate future expansion for different geographic coding systems, allowing capability providers to select the appropriate coding type for return based on actual situations.\ + + **codeValue**: String type, representing the specific encoding value of the corresponding codeType. For example, when codeType is `Postal Code`, codeValue may be a postal code similar to "100000". It, together with the countryCode and codeType, forms a complete location identifier that accurately points to a specific geographic area. + + # Identifying a device from the access token + + This specification defines the `device` object field as optional in API requests, specifically in cases where the API is accessed using a 3-legged access token, and the device can be uniquely identified by the token. This approach simplifies API usage for API consumers by relying on the device information associated with the access token used to invoke the API. + + ## Handling of device information: + + ### Optional device object for 3-legged tokens: + + - When using a 3-legged access token, the device associated with the access token must be considered as the device for the API request. This means that the device object is not required in the request, and if included it must identify the same device, therefore **it is recommended NOT to include it in these scenarios** to simplify the API usage and avoid additional validations. + + ### Validation mechanism: + + - The server will extract the device identification from the access token, if available. + + - If the API request additionally includes a `device` object when using a 3-legged access token, the API will validate that the device identifier provided matches the one associated with the access token. + + - If there is a mismatch, the API will respond with a `403 - INVALID_TOKEN_CONTEXT` error, indicating that the device information in the request does not match the token. + + ### Error handling for unidentifiable devices: + + - If the `device` object is not included in the request and the device information cannot be derived from the 3-legged access token, the server will return a 422 `UNIDENTIFIABLE_DEVICE` error. + + ### Restrictions for tokens without an associated authenticated identifier: + + - For scenarios which do not have a single device identifier associated to the token during the authentication flow, e.g. 2-legged access tokens, the `device` object MUST be provided in the API request. This ensures that the device identification is explicit and valid for each API call made with these tokens. + termsOfService: http://swagger.io/terms/ + contact: + email: sp-location-insights@lists.camaraproject.org + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ +servers: + - url: "{apiRoot}/device-visit-location/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: DeviceVisitLocation + description: Operations to retrieve device visit location information. +paths: + /retrieve: + post: + security: + - openId: + - device-visit-location:retrieve + tags: + - DeviceVisitLocation + summary: Retrieves device visit location information + description: Retrieves the latest visit locations of a device within a given + time window. + operationId: retrieveDeviceVisitLocation + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveVisitLocationRequest" + example: + device: + phoneNumber: "+123456789" + startTime: 2024-04-23T14:44:18.165Z + endTime: 2024-04-30T14:44:18.165Z + responses: + "200": + description: Device Visit Location query result + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveVisitLocationResponse" + example: + geoCodeList: + - countryCode: CN + codeType: PostalCode + codeValue: "110000" + - countryCode: CN + codeType: PostalCode + codeValue: "310000" + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/RetrieveVisitLocationBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/RetrieveVisitLocationNotFound404" + "422": + $ref: "#/components/responses/Generic422" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" +components: + securitySchemes: + openId: + type: openIdConnect + description: to support Consent Management + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + schemas: + RetrieveVisitLocationRequest: + type: object + description: Request with a device as identifier,starttime and endtime + required: + - startTime + - endTime + properties: + device: + $ref: "#/components/schemas/Device" + startTime: + type: string + format: date-time + description: Start date time of the time window. If not provided, the default is + the past seven days from the request time. It must follow [RFC + 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and + must have time zone. Recommended format is + yyyy-MM-dd'T'HH:mm:ss.SSSZ. + endTime: + type: string + format: date-time + description: End date time of the time window. If not provided, the default is + the past seven days from the request time. It must follow [RFC + 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and + must have time zone. Recommended format is + yyyy-MM-dd'T'HH:mm:ss.SSSZ. + RetrieveVisitLocationResponse: + type: object + description: Contains the list of geoCode objects representing the visited locations. + required: + - geoCodeList + properties: + geoCodeList: + type: array + items: + $ref: "#/components/schemas/geoCode" + minItems: 1 + geoCode: + type: object + properties: + countryCode: + type: string + description: Code for the country where the location is is located. Following + the `ISO 3166 ALPHA-2` standard, for example, "CN" represents China, + "US" represents the United States, etc. + codeType: + type: string + description: The type of code.This field is used to specify the geographic + encoding type used, with a fixed value of `PostlCode` in the current + version. + codeValue: + type: string + description: The actual value of the code,representing the specific encoding + value of the corresponding codeType. + required: + - countryCode + - codeType + - codeValue + Device: + description: >- + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + + * `ipv6Address` + + * `phoneNumber` + + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: ^\+[1-9][0-9]{4,14}$ + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. + In 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the + telephone number, the network access identifier is not subjected to + portability ruling in force, and is individually managed by each + operator. + type: string + example: 123456789@domain.com + DeviceIpv4Addr: + type: object + description: >- + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: + - publicAddress + - privateAddress + - required: + - publicAddress + - publicPort + example: + publicAddress: 84.125.93.10 + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: 84.125.93.10 + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: The device should be identified by the observed IPv6 address, or by + any single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + ErrorInfo: + type: object + description: Error information + required: + - message + - status + - code + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + responses: + RetrieveVisitLocationBadRequest400: + description: >- + Bad Request. + + In addition to regular scenario of `INVALID_ARGUMENT`, other scenarios may exist: + + - Indicated endTime is earlier than the startTime ("code": "DEVICE_VISIT_LOCATION.INVALID_END_DATE","message": "Indicated endTime is earlier than the startTime.") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - DEVICE_VISIT_LOCATION.INVALID_END_DATE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_END_DATE: + value: + status: 400 + code: DEVICE_VISIT_LOCATION.INVALID_END_DATE + message: Indicated endTime is earlier than the startTime. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required + scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the + API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + RetrieveVisitLocationNotFound404: + description: >- + Not found. + + In addition to regular scenario of `NOT_FOUND`, other scenarios may exist: + + - Device identifier not found ("code": "DEVICE_NOT_FOUND","message": "Device identifier not found."). + + - Unable to find the visit location information of the device within the given time window, it may be due to the device being offline ("code": "DEVICE_VISIT_LOCATION.DATA_NOT_FOUND","message": "Unable to find the visit location information of the device within the given time window"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + - DEVICE_VISIT_LOCATION.DATA_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + DATA_NOT_FOUND: + description: Unable to find the visit location information of the device within + the given time window + value: + status: 404 + code: DEVICE_VISIT_LOCATION.DATA_NOT_FOUND + message: Unable to find the visit location information of the device within the + given time window. + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 405 + code: + enum: + - METHOD_NOT_ALLOWED + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 406 + code: + enum: + - NOT_ACCEPTABLE + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) + indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by + the client through `Accept-*` headers. + Generic412: + description: Failed precondition + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 412 + code: + enum: + - FAILED_PRECONDITION + examples: + GENERIC_412_FAILED_PRECONDITION: + description: Indication by the API Server that the request cannot be processed + in current system state + value: + status: 412 + code: FAILED_PRECONDITION + message: Request cannot be executed in the current system state. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or + phone number identification cannot be derived from the 3-legged + access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number + has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as + far as possible to get the objective to reach aligned + implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 502 + code: + enum: + - BAD_GATEWAY + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage + the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to + maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 504 + code: + enum: + - TIMEOUT + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. +``` diff --git a/marked/DeviceVisitLocation/documentation/API_documentation/README/raw.md b/marked/DeviceVisitLocation/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceVisitLocation/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/DeviceVisitLocation/documentation/SupportingDocuments/README/raw.md b/marked/DeviceVisitLocation/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/DeviceVisitLocation/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/EdgeApplicationManagement/README/raw.md b/marked/EdgeApplicationManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d367de4def404d3082a3c0488e2e351934dc60fb --- /dev/null +++ b/marked/EdgeApplicationManagement/README/raw.md @@ -0,0 +1,42 @@ + + + + + + + + + +# EdgeApplicationManagement + +Sandbox API Repository to describe, develop, document, and test the EdgeApplicationManagement Service API(s) within the Sub Project [EdgeCloud](https://lf-camaraproject.atlassian.net/wiki/x/ujLe). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) !! to be updated when wiki page for the repository is created + +## Scope + +* Service API “EdgeApplicationManagement” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * Manage the lifecycle of Edge applications and instances + * Discover an operator's Edge Cloud zones and their status. +* Describe, develop, document, and test the API(s) +* Started: May 2024 (as part of the [Edge Cloud](https://github.com/camaraproject/EdgeCloud) sub project) + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/EdgeApplicationManagement/code/API_definitions/README/raw.md b/marked/EdgeApplicationManagement/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/EdgeApplicationManagement/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/EdgeApplicationManagement/documentation/API_documentation/README/raw.md b/marked/EdgeApplicationManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/EdgeApplicationManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/EdgeApplicationManagement/documentation/SupportingDocuments/README/raw.md b/marked/EdgeApplicationManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/EdgeApplicationManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/EdgeCloud/README/raw.md b/marked/EdgeCloud/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fd3d987dda36021dffc4355f6c0207c58491bc84 --- /dev/null +++ b/marked/EdgeCloud/README/raw.md @@ -0,0 +1,52 @@ + + + + + + + + + +# EdgeCloud + +Sandbox API Repository to describe, develop, document, and test Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) +* Warning + +> [!WARNING] +> After the CAMARA Spring25 meta release, the following APIs have been separated into 5 individual repositories: +> - [SimpleEdgeDiscovery](https://github.com/camaraproject/SimpleEdgeDiscovery) +> - [ApplicationEndpointDiscovery](https://github.com/camaraproject/ApplicationEndPointDiscovery) +> - [TrafficInfluence](https://github.com/camaraproject/TrafficInfluence) +> - [ApplicationEndpointRegistration](https://github.com/camaraproject/ApplicationEndpointRegistration) +> - [OptimalEdgeDiscovery](https://github.com/camaraproject/OptimalEdgeDiscovery) +> +> **For these APIs:** This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + +**For the EdgeApplicationManagement API:** API development will continue in this repository until further notice + +## Scope + +* Service APIs for “Edge Cloud” (see APIBacklog.md) +* It provides the customer with the ability to: + * Discover the closest edge cloud zone to a given device (https://github.com/camaraproject/SimpleEdgeDiscovery). + * Provide and manage application images to be deployed on resources within the operator network. + * Use reserved compute resources within the operator network for the deployment of applications on VMs or containers. + * Influence the traffic routing from the user device toward the Edge instance of the Application (https://github.com/camaraproject/TrafficInfluence). + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: 5th July 2022 + +# Release Information + +# Contributing + +* Meetings + * [Registration](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Schedule: Tuesdays 1400-1500 UTC, every two weeks. + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/Edge+Cloud) + +* Mailing list + * Subscribe / unsubscribe to the mailing list of this Sub Project [https://lists.camaraproject.org/g/sp-edc](https://lists.camaraproject.org/g/sp-edc). + * A message to the community of this Sub Project can be sent using [sp-edc@lists.camaraproject.org](sp-edc@lists.camaraproject.org). diff --git a/marked/EdgeCloud/code/API_definitions/edge-application-management/raw.md b/marked/EdgeCloud/code/API_definitions/edge-application-management/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..99ffb71affa69de4a825acb20e74c0d6f0ead508 --- /dev/null +++ b/marked/EdgeCloud/code/API_definitions/edge-application-management/raw.md @@ -0,0 +1,2045 @@ +# edge-application-management + +```yaml +--- +openapi: 3.0.3 +info: + title: Edge Application Management API + version: wip + description: | + Edge Application Management API allows API consumers to manage the + Life Cycle of an Application and to Discover Edge Cloud Zones. + # Overview + The reference scenario foresees a distributed Telco Edge Cloud where any + Application Delevoper, known as an Application Provider, can host and + deploy their application according to their specifications and operational + criteria (e.g. within an specific geographical zone for data protection + purposes, ensure a minimum QoS for the application clients, etc). + Through Telco Edge Cloud services Developers around the globe can be + benefit from the traditional Cloud strengths but expertise and advantages + of the Mobile Network Operators offering to their users an evolved + experience for XR, V2X, Holographic and other new services. + + # Introduction + The Edge Application Management API provides capabilities for lifecycle + management of application, instances and edge cloud zone discovery. + Lifecycle Management allows Application Provider to onboard + their application to the Edge Cloud Platform which do bookkeeping, + resource validation and other pre-deployment operations. + Application details can contain components network specification, + package type (QCOW2, OVA, CONTAINER, HELM, CSAR), operating system details and + respository to download the image of the desired application. + Once the application is available on the Edge Cloud + Platform, the Application Provider can instantiate the application. + Edge Cloud Provider helps Application Provider to decide where to + instantiate the applications allowing them to retrieve a list of + Edge Cloud Zones that meets the provided criteria. + + This discovery can be filtered by an specific geographical region + (e.g when data residency is need) and by status (active, inactive, unknown) + Application Provider can ask the Edge Cloud Platform to instantiate the + application to one or several Edge Cloud Zones that meet the criteria. + Typically when more than one Edge Cloud Zone is required in the same + geographic boundary, Application Provider can define instead + the entire Edge Cloud Region. + + Application Provider can retrieve the information of the instances + for a given application, the information could be the Edge Cloud Zone + where the instance is, status (ready, instantiating, failed, + terminating, unknown) and endpoint (ip, port, fqdn). + Application Provider can terminate an instance of an application + (appInstanceId) or all the instances for a given appId. + + # Quick Start + The usage of this API is based on several resources including GSMA + Edge Platform, Public Cloud and SDOs, to define a first approach on the + lifecycle management of application instances and edge cloud zones discovery + + Before starting to use the API, the developer needs to know about + the below specified details. + + __Application Management__ + * __submitApp__ - Submits application details to an Edge Cloud Provider. + Based on the details provided, Edge Cloud Provider shall do bookkeeping, + resource validation and other pre-deployment operations. + * __deleteApp__ - Removes an application from an Edge Cloud Provider, + if there is a running instance of the given application, + the request cannot be done. + * __getApp__ - Retrieves the information of a given application. + + __Application Instance Management__ + * __createAppInstance__ Request the Edge Cloud Provider to instatiate + an instance of an application in a given Edge Cloud Zone, + if this parameter is not set, the Edge Cloud Provider will instantiate + the applications in all the Edge Cloud Zones. + * __getAppInstance__ Retrieves the list with information of the instances + related to a given application. + * __deleteAppInstance__ - Removes a given application instance from an Edge + Cloud Zone. + + __Application Deployment Management__ + * __createAppDeployment__ - Requests the Edge Cloud Provider to create and + maintain application instances to multiple Edge Cloud Zones. + * __getAppDeployments__ - Retrieves a list of deployments for a given + application. + * __deleteAppDeployment__ - Terminates a specific application deployment, + removing all associated instances. + + __Edge Cloud information__ + * __getEdgeCloudZones__ List of the operators Edge Cloud Zones and their + status, ordering the results by location and filtering by status + (active/inactive/unknown) + + # Authentication and Authorization + CAMARA guidelines defines a set of authorization flows which can grant API + clients access to the API functionality, as outlined in the document + [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject\ + /IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access\ + -and-user-consent.md). + Which specific authorization flows are to be used will be determined during + onboarding process, happening between the API Client and the Telco Edge + exposing the API, taking into account the declared purpose for accessing the + API, while also being subject to the prevailing legal framework dictated by + local legislation. + + It is important to remark that in cases where personal user data is + processed by the API, and users can exercise their rights through mechanisms + such as opt-in and/or opt-out, the use of 3-legged access tokens becomes + mandatory. This measure ensures that the API remains in strict compliance + with user privacy preferences and regulatory obligations, upholding the + principles of transparency and user-centric data control. + # API documentation + Two operations have been defined in Edge Application Management API. + + *__Application__* - The Application Provider submit application metadata to + the Edge Cloud Platform. The Edge Cloud Platform generates an appId for that + metadata that will be used to instantiate the application within + the Edge Cloud Zone. + + *__Edge Cloud__* - Retrieves all the Edge Cloud Zones available according to + some defined parameters where an application can be instantiated. + + Definitions of terminologies commonly referred + to throughout the API descriptions. + * __Application Provider__ - The provider of the application that accesses + an Edge Cloud Provider to deploy its application on the Edge Cloud. + An Application Provider may be part of a larger organisation, + like an enterprise, enterprise customer of an Edge Cloud Provider, + or be an independent entity. + * __Application__ - Contains the information about the application to be + instantiated. Descriptor, binary image, charts or any other package + assosiated with the application. The Application Provider request contains + mandatory criteria (e.g. required CPU, memory, storage, bandwidth) defined + in an Application. The Edge Cloud Platform generates a unique ID + for an Application that is ready to be instantiated. + * __Application Instance__ - Is an instance (VM or Container based) running + in an Edge Cloud Zone. The Edge Cloud Platform generates a unique ID + for each instance. + * __Application Deployment__ - A specification that defines the requirements + for the Edge Cloud Provider to create and maintain application instances + across multiple Edge Cloud Zones. The deployment ensures that the + application is instantiated and managed consistently across the specified + zones, meeting the defined requirements. + * __Edge Cloud__ - Cloud-like capabilities located at the network edge + including, from the Application Provider's perspective, access to + elastically allocated compute, data storage and network resources, + this access is provided through the Edge Cloud Platform. + * __Edge Cloud Provider__ - Company name of the provider offering the + Edge Services through the Edge Cloud Platform. + Could be an Operator or a Cloud Provider. + * __Edge Cloud Region__ - An Edge Cloud Region is equivalent + to a Region on a Public Cloud. + The higher construct in the hierarchy exposed to an Application + Provider who wishes to deploy an Application on the Edge Cloud and broadly + represents a geography. An Edge CloudRegion typically contains one or + multiple Edge Cloud Zones. + An Edge Cloud Region exists within an Edge Cloud. + * __Edge Cloud Zone__ - An Edge Cloud Zone is the lowest level of + abstraction exposed to an Application Provider who wants to deploy + an Application on Edge Cloud. + Edge Cloud Zones exists within a Edge Cloud Region. + --- + contact: + email: sp-edc@lists.camaraproject.org + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/EdgeCloud + +servers: + - url: "{apiRoot}/edge-application-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application + description: Application and Application Instance Lice Cycle Management + - name: Edge Cloud + description: Edge Cloud Zones Availability + +paths: + /apps: + post: + security: + - openId: + - edge-application-management:apps:write + tags: + - Application + summary: Submit application metadata to the Edge Cloud Provider. + description: | + Contains the information about the application to be + instantiated in the Edge Cloud + operationId: submitApp + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + The Application Provider request contains mandatory + criteria (e.g. required CPU, memory, storage, bandwidth) and + optional parameters. + content: + application/json: + schema: + $ref: '#/components/schemas/AppManifest' + required: true + responses: + '201': + description: Application created successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/SubmittedApp' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "App already exists" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:apps:read + tags: + - Application + summary: Retrieve a list of existing Applications + description: | + Get the list of all existing Application definitions from the + Edge Cloud Provider that the user has permission to view. + operationId: getApps + parameters: + - $ref: '#/components/parameters/x-correlator' + responses: + '200': + description: List of existing applications + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppManifest' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /apps/{appId}: + get: + security: + - openId: + - edge-application-management:apps:read + tags: + - Application + summary: Retrieve the information of an Application + description: | + Ask the Edge Cloud Provider the information for a given application + operationId: getApp + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with the + application. + Edge Cloud Provider generates this identifier when the application + is submitted. + in: path + required: true + schema: + $ref: '#/components/schemas/AppId' + responses: + '200': + description: Information of Application + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: object + properties: + appManifest: + $ref: '#/components/schemas/AppManifest' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + delete: + security: + - openId: + - edge-application-management:apps:delete + tags: + - Application + summary: | + Delete an Application from an Edge Cloud Provider + description: Delete all the information and content + related to an Application + operationId: deleteApp + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + in: path + description: | + Identificator of the application to be + deleted provided by the Edge Cloud Provider + once the submission was successful + required: true + schema: + $ref: "#/components/schemas/AppId" + responses: + '202': + description: Request accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '204': + description: App deleted + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "App with a running application instance + cannot be deleted" + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /appinstances: + post: + security: + - openId: + - edge-application-management:instances:write + tags: + - Application + summary: Instantiation of an Application + description: | + Ask the Edge Cloud Platform to instantiate an application to an + Edge Cloud Zone. + operationId: createAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Information about the application and where to deploy it. + content: + application/json: + schema: + type: object + required: + - name + - appId + - edgeCloudZoneId + properties: + name: + $ref: '#/components/schemas/AppInstanceName' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + required: true + responses: + '202': + description: Application instantiation accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Location: + description: Contains the URI of the newly created application. + required: true + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/AppInstanceInfo' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Application already instantiated in the given + Edge Cloud Zone" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:instances:read + tags: + - Application + summary: Retrieve the information of Application Instances for a given App + description: | + Ask the Edge Cloud Provider the information of the instances for a + given application + operationId: getAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with + the application. + Edge Cloud Provider generates this identifier when the + application is submitted. + in: query + required: false + schema: + $ref: '#/components/schemas/AppId' + - name: appInstanceId + description: | + A globally unique identifier associated with a running + instance of an application within an specific Edge Cloud Zone. + Edge Cloud Provider generates this identifier. + in: query + required: false + schema: + $ref: '#/components/schemas/AppInstanceId' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + responses: + '200': + description: | + List of application instances. Returns an empty list if no + instances were found or none match the specified query + parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppInstanceInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /appinstances/{appInstanceId}: + delete: + security: + - openId: + - edge-application-management:instances:delete + tags: + - Application + summary: Terminate an Application Instance + description: | + Terminate a running instance of an application within + an Edge Cloud Zone + operationId: deleteAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appInstanceId + in: path + description: | + Identificator of the specific application instance + that will be terminated + required: true + schema: + $ref: "#/components/schemas/AppInstanceId" + responses: + '202': + description: | + Request accepted to be processed. It applies for async + deletion process + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '204': + description: Application Instance Deleted + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /deployments: + post: + security: + - openId: + - edge-application-management:deployments:write + tags: + - Application + summary: Deploy an Application + description: | + Ask the Edge Cloud Platform to instantiate an application to several + Edge Cloud Zones. + operationId: createAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Information about the application and where to deploy it. + content: + application/json: + schema: + type: object + required: + - appDeploymentName + - appId + - edgeCloudZones + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRefs: + type: array + items: + $ref: '#/components/schemas/KubernetesClusterRef' + required: true + responses: + '202': + description: Application deployment accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: object + properties: + appDeploymentId: + $ref: '#/components/schemas/AppDeploymentId' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Deployment already exists" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:deployments:read + tags: + - Application + summary: Retrieve a list of Application Deployment for a given App + description: | + Ask the Edge Cloud Provider the information of the Deployments for a + given application + operationId: getAppDeployments + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with + the application. + Edge Cloud Provider generates this identifier when the + application is submitted. + in: query + required: false + schema: + $ref: '#/components/schemas/AppId' + - name: appDeploymentId + description: | + A globally unique identifier associated with a existing deployment + of an application. Edge Cloud Platform generates this identifier when + the deployment request in the Edge Cloud Zone is successful. + in: query + required: false + schema: + $ref: '#/components/schemas/AppDeploymentId' + responses: + '200': + description: | + List of application deployments. Returns an empty list if no + deployments were found or none match the specified query + parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppDeploymentInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /deployments/{appDeploymentId}: + delete: + security: + - openId: + - edge-application-management:deployments:delete + tags: + - Application + summary: Terminate an Application Deployment + description: | + Delete a deployment terminating all related instances of an application + operationId: deleteAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appDeploymentId + in: path + description: | + Identificator of the specific application deployment + that will be terminated + required: true + schema: + $ref: "#/components/schemas/AppDeploymentId" + responses: + '202': + description: | + Request accepted to be processed. It applies for async + deletion process + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + patch: + security: + - openId: + - edge-application-management:deployments:update + tags: + - Application + summary: Update an Application Deployment + description: | + Update the configuration or properties of an existing application deployment + using JSON Merge Patch semantics (RFC 7396). Only the fields provided in the + request body will be updated. Fields not included in the request will remain unchanged. + + IMPORTANT: When updating array fields (like edgeCloudZones or kubernetesClusterRefs), + JSON Merge Patch will REPLACE the entire array, not merge or append to it. + + This operation may include changing the deployment name, target Edge Cloud Zones, or other updatable fields. + operationId: updateAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appDeploymentId + in: path + description: | + Identifier of the specific application deployment to be updated. + required: true + schema: + $ref: "#/components/schemas/AppDeploymentId" + requestBody: + description: | + The fields to update for the application deployment using JSON Merge Patch (RFC 7396). + Only the fields included in the request will be updated; omitted fields remain unchanged. + + NOTE: When updating array fields (edgeCloudZones, kubernetesClusterRefs), the entire array + will be REPLACED, not merged. To modify an array, you must include the complete array + with all desired elements in your request. + required: true + content: + application/merge-patch+json: + schema: + type: object + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRefs: + type: array + items: + $ref: '#/components/schemas/KubernetesClusterRef' + examples: + updateDeploymentName: + summary: Update only the deployment name + description: | + This example shows how to update only the deployment name. + Other fields will remain unchanged. + value: + appDeploymentName: "my_updated_deployment" + updateMultipleFields: + summary: Update multiple fields simultaneously + description: | + This example shows how to update both the deployment name + and Edge Cloud Zones in a single request. Remember that both + array fields will be completely replaced with the new values. + value: + appDeploymentName: "production_deployment" + edgeCloudZones: + - "123e4567-e89b-12d3-a456-426614174000" + - "123e4567-e89b-12d3-a456-426614174001" + kubernetesClusterRefs: + - "642f6105-7015-4af1-a4d1-e1ecb8437abc" + - "642f6105-7015-4af1-a4d1-e1ecb8437def" + arrayReplacementExample: + summary: Example of array replacement behavior + description: | + This example demonstrates how arrays are completely replaced in JSON Merge Patch. + + If the current deployment has: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174001", "123e4567-e89b-12d3-a456-426614174002"] + - kubernetesClusterRefs: ["642f6105-7015-4af1-a4d1-e1ecb8437abc", "642f6105-7015-4af1-a4d1-e1ecb8437def"] + + And the user sends this patch: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174003"] + + The result will be: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174003"] (completely replaced) + - kubernetesClusterRefs: ["642f6105-7015-4af1-a4d1-e1ecb8437abc", "642f6105-7015-4af1-a4d1-e1ecb8437def"] (unchanged, as it wasn't in the patch) + + To add a single zone while keeping existing ones, ALL zones must be included in the request. + value: + edgeCloudZones: + - "123e4567-e89b-12d3-a456-426614174000" + - "123e4567-e89b-12d3-a456-426614174003" + responses: + '200': + description: Application deployment updated successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/AppDeploymentInfo' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Update conflict" + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /clusters: + get: + security: + - openId: + - edge-application-management:clusters:read + tags: + - Cluster + summary: | + Retrieve a list of the available clusters filtered by the optional + query parameters. + description: | + List available cluster information + operationId: getClusters + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Cluster. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + - name: clusterRef + description: | + A globally unique identifier for the Cluster. + in: query + required: false + schema: + $ref: '#/components/schemas/KubernetesClusterRef' + - name: edgeCloudZoneId + description: | + Edge Cloud Zone identifier. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudZoneId' + responses: + '200': + description: | + Successful response, returning the cluster's information. + Returns an empty list if no clusters were found or none match + the specified query parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/ClusterInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /edge-cloud-zones: + get: + security: + - openId: + - edge-application-management:edge-cloud-zones:read + tags: + - Edge Cloud + summary: Retrieve a list of the operators Edge Cloud Zones and + their status + description: | + List of the operators Edge Cloud Zones and their + status, ordering the results by location and filtering by + status (active/inactive/unknown) + operationId: getEdgeCloudZones + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + - name: status + description: Human readable status of the Edge Cloud Zone + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudZoneStatus' + responses: + '200': + description: | + Successful response, returning the + Available Edge Cloud Zones. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/EdgeCloudZones' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' +components: + securitySchemes: + openId: + description: OpenID Provider Configuration Information. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: | + Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: | + Correlation id for the different services + required: false + schema: + type: string + format: uuid + + schemas: + AccessEndpoint: + type: object + description: | + Application Endpoint for an especific instance that is + running in an specific Edge Cloud Zone. + required: + - port + anyOf: + - required: + - fqdn + - required: + - ipv4Addresses + - required: + - ipv6Addresses + properties: + port: + $ref: '#/components/schemas/Port' + fqdn: + $ref: '#/components/schemas/Fqdn' + ipv4Addresses: + description: IP version 4 of an application instance + type: array + items: + $ref: '#/components/schemas/Ipv4Addr' + minItems: 1 + ipv6Addresses: + description: IP version 6 of an application instance. + type: array + items: + $ref: '#/components/schemas/Ipv6Addr' + minItems: 1 + + AppId: + type: string + format: uuid + description: | + A globally unique identifier associated with the application. + Edge Cloud Platform generates this identifier when the + Application is submitted. + + AppInstanceId: + type: string + format: uuid + description: | + A globally unique identifier associated with a running + instance of an application. + Edge Cloud Platform generates this identifier when the + instantiation in the Edge Cloud Zone is successful. + + AppDeploymentId: + type: string + format: uuid + description: | + A globally unique identifier associated with a existing deployment + of an application. Edge Cloud Platform generates this identifier when + the deployment request in the Edge Cloud Zone is successful. + + AppDeploymentInfo: + type: object + required: + - appDeploymentName + - appDeploymentId + - appId + - edgeCloudZones + - appInstances + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + appDeploymentId: + $ref: '#/components/schemas/AppDeploymentId' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + appInstances: + type: array + items: + $ref: '#/components/schemas/AppInstanceId' + + AppInstanceInfo: + description: Information about the application instance. + type: object + required: + - name + - appId + - appInstanceId + - appProvider + - edgeCloudZoneId + properties: + name: + $ref: '#/components/schemas/AppInstanceName' + appId: + $ref: '#/components/schemas/AppId' + appInstanceId: + $ref: '#/components/schemas/AppInstanceId' + appProvider: + $ref: '#/components/schemas/AppProvider' + status: + description: Status of the application instance (default is 'unknown') + type: string + enum: + - ready + - instantiating + - failed + - terminating + - unknown + default: unknown + componentEndpointInfo: + description: | + Information about the IP and Port exposed by the + Edge Cloud Platform. + Application Client shall use these access points to reach this + application instance + type: array + items: + type: object + required: + - interfaceId + - accessPoints + properties: + interfaceId: + type: string + pattern: ^[A-Za-z0-9][A-Za-z0-9_]{6,30}[A-Za-z0-9]$ + description: | + This is the interface Identifier that Application Provider + defines when application is being submitted. + accessPoints: + $ref: '#/components/schemas/AccessEndpoint' + minItems: 1 + kubernetesClusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + + AppInstanceName: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the App instance, scoped to the AppProvider + + AppDeploymentName: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the App Deployment, scoped to the AppProvider + + AppManifest: + description: | + Application information and requirements provided by the + Application Provider + properties: + appId: + $ref: '#/components/schemas/AppId' + name: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the application. + appProvider: + $ref: '#/components/schemas/AppProvider' + version: + type: string + description: Application version information + packageType: + description: Format of the application image package + type: string + enum: + - QCOW2 + - OVA + - CONTAINER + - HELM + - CSAR + operatingSystem: + $ref: '#/components/schemas/OperatingSystem' + appRepo: + description: | + Repository where Application Provider stores the application image + type: object + required: + - type + - imagePath + properties: + type: + type: string + enum: + - PRIVATEREPO + - PUBLICREPO + description: | + Application repository and image URI information. + PUBLICREPO is used of public urls like github, helm repo etc. + PRIVATEREPO is used for private repo managed by the application + developer. Private repo can be accessed by using the app + developer provided userName and password. Password is + recommended to be the personal access token created by developer + e.g. in Github repo. + imagePath: + $ref: '#/components/schemas/Uri' + userName: + type: string + description: | + Username to acces the Helm chart, docker-compose + file or VM image repository + credentials: + type: string + maxLength: 128 + description: | + Password or personal access token created by + developer to acces the app repository. API users can generate + a personal access token e.g. docker clients to use them as + password. + authType: + type: string + enum: + - DOCKER + - HTTP_BASIC + - HTTP_BEARER + - NONE + description: | + The credentials can also be formatted as a Basic + auth or Bearer auth in HTTP "Authorization" header. + checksum: + type: string + description: | + MD5 checksum for VM and file-based images, sha256 + digest for containers + requiredResources: + $ref: '#/components/schemas/RequiredResources' + componentSpec: + description: | + Information defined in "appRepo" point to the application + descriptor e.g. Helm chart, docker-compose yaml file etc. + The descriptor may contain one or more containers and their + associated meta-data. A component refers to additional details + about these containers to expose the instances of the containers + to external client applications. App provider can define one or + more components (via the associated network port) in componentSpec + corresponding to the containers in helm charts or docker-compose + yaml file as part of app descriptors. + type: array + items: + type: object + required: + - componentName + - networkInterfaces + properties: + componentName: + type: string + description: Component name must be unique with an application + networkInterfaces: + description: | + Each application component exposes some ports + either for external users or for inter component + communication. + Application provider is required to specify which ports are + to be exposed and the type of traffic that will flow through + these ports.The underlying platform may assign a dynamic port + against the "extPort" that the application clients will use + to connect with edge application instance. + type: array + items: + type: object + required: + - interfaceId + - protocol + - port + - visibilityType + properties: + interfaceId: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{3,31}$ + description: | + Each Port and corresponding traffic protocol + exposed by the component is identified by a name. + Application client on user device requires this to + uniquley idenify the interface. + protocol: + type: string + enum: + - TCP + - UDP + - ANY + description: | + Defines the IP transport communication + protocol i.e., TCP, UDP or ANY + port: + type: integer + format: int32 + minimum: 1 + maximum: 65535 + description: | + Port number exposed by the component. + Edge Cloud Provider may generate a dynamic port + towards the component instance which forwards + external traffic to the component port. + visibilityType: + description: | + Defines whether the interface is exposed + to outer world or not i.e., external, or internal. + If this is set to "external", then it is exposed + to external applications otherwise it is exposed + internally to edge application components within + edge cloud. When exposed to external world, + an external dynamic port is assigned for UC traffic + and mapped to the extPort + type: string + enum: + - VISIBILITY_EXTERNAL + - VISIBILITY_INTERNAL + minItems: 1 + required: + - name + - version + - appProvider + - packageType + - appRepo + - requiredResources + - componentSpec + + AppProvider: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{7,63}$ + description: Human readable name of the Application Provider. + + ClusterInfo: + description: Kubernetes cluster information + required: + - name + - provider + - clusterRef + - edgeCloudZoneId + properties: + name: + type: string + description: | + Name of the Cluster, scoped to the Provider + provider: + $ref: '#/components/schemas/AppProvider' + clusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + version: + type: string + description: Kubernetes version of the cluster. + nodePools: + description: Node Pools in the cluster. + type: array + items: + $ref: '#/components/schemas/KubernetesNodePool' + minItems: 1 + + EdgeCloudProvider: + type: string + description: Human readable name of the Edge Cloud Provider. + + EdgeCloudRegion: + type: string + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + + EdgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZone' + minItems: 1 + description: | + A collection of Edge Cloud Zones where the Application Provider can + instantiate an Application Instance. + additionalProperties: false + + EdgeCloudZoneId: + type: string + format: uuid + description: | + Unique identifier created by the Edge Cloud Platform to identify an + Edge Cloud Zone within an Edge Cloud. + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + edgeCloudZoneName: + $ref: '#/components/schemas/EdgeCloudZoneName' + edgeCloudZoneStatus: + $ref: '#/components/schemas/EdgeCloudZoneStatus' + edgeCloudProvider: + $ref: '#/components/schemas/EdgeCloudProvider' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + minItems: 1 + + EdgeCloudZoneName: + type: string + description: | + Human readable name of the geographical zone of + the Edge Cloud. Defined by the Edge Cloud Provider. + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + ErrorInfo: + type: object + description: Information about the error + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + Fqdn: + type: string + description: | + Full qualified domain name of an application instance + + GpuInfo: + type: object + description: Information about the supported GPUs + required: + - gpuMemory + - numGPU + properties: + gpuMemory: + type: integer + description: GPU memory in mega bytes + numGPU: + type: integer + description: Number of GPUs + + K8sAddons: + description: | + Addons for the Kubernetes cluster. + Additional addons should be defined in application the helm chart + (Service Mesh, Serverless, AI). + type: object + properties: + monitoring: + type: boolean + example: true + default: false + description: Enable monitoring for Kubernetes cluster. + ingress: + type: boolean + example: true + default: false + description: Enable ingress for Kubernetes cluster. + + K8sNetworking: + description: | + Kubernetes networking definition + type: object + properties: + primaryNetwork: + description: Definition of Kubernetes primary Network + type: object + properties: + provider: + description: CNI provider name + type: string + example: cilium + version: + description: CNI provider version + type: string + example: "1.13" + additionalNetworks: + description: Additional Networks for the Kubernetes cluster. + type: array + items: + type: object + description: Additional network interface definition + properties: + name: + description: Additional Network Name + type: string + example: net1 + interfaceType: + description: | + Type of additional Interface: + netdevice: (SR-IOV) A regular kernel network device in the + Network Namespace (netns) of the container + vfio-pci: (SR-IOV) A PCI network interface directly mounted + in the container + interface: Additional interface to be used by cni plugins + such as macvlan, ipvlan + Note: The use of SR-IOV interfaces automatically + configure the required kernel parameters for the nodes. + type: string + example: vfio-pci + enum: + - netdevice + - vfio-pci + - interface + + AdditionalStorage: + description: Additional storage for the application. + type: array + items: + type: object + required: + - storageSize + - mountPoint + properties: + name: + type: string + description: Name of additional storage resource. + example: logs + storageSize: + type: string + description: Additional persistent volume for the application. + example: 80GB + pattern: ^\d+(GB|MB)$ + mountPoint: + type: string + description: Location of additional storage resource. + example: /logs + + Vcpu: + type: string + pattern: ^\d+((\.\d{1,3})|(m))?$ + description: | + Number of vcpus in whole (i.e 1), decimal (i.e 0.500) up to + millivcpu, or millivcpu (i.e 500m) format. + example: "500m" + + KubernetesClusterRef: + description: | + A global unique identifier associated with a Kubernetes cluster + infrastructure. + type: string + format: uuid + example: "642f6105-7015-4af1-a4d1-e1ecb8437abc" + + KubernetesNodePool: + description: | + A Kubernetes node pool is a set of Kubernetes nodes that have the + same configuration (vCPU, memory, networking, OS, etc) on each node. + required: + - name + - numNodes + - nodeResources + - scalable + properties: + name: + description: Human readable name of the Kubernetes Node Pool. + type: string + numNodes: + description: Number of nodes in the Node Pool. + type: integer + scalable: + description: | + Indicates if the node pool can be dynamically scaled up by the + system to accomodate more applications, and dynamically scaled + down by the system when there are unused resources. + type: boolean + example: false + nodeResources: + description: Resource configuration of a node. + type: object + required: + - numCPU + - memory + properties: + numCPU: + description: | + Number of whole vcpus for the node. + type: integer + example: 2 + memory: + description: | + Amount of system memory in mega bytes for the node. + type: integer + example: 4096 + + KubernetesResources: + description: Definition of Kubernetes Cluster Infrastructure. + required: + - infraKind + - applicationResources + - isStandalone + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: kubernetes + enum: + - kubernetes + applicationResources: + description: | + Application resources define the resources pool required + by the application to be executed in a Kubernetes clusters. + type: object + properties: + cpuPool: + required: + - numCPU + - memory + - topology + type: object + description: | + CPU Pool refers to the amount of application' resources + that is executed in nodes with CPU only. That means the part + of application that doesn't require GPU or other kind of + acceleration. + CPU pool is not mandatory when the application is executed + exclusively in a GPU pool. + A CPU pool is composed by CPU and memory. + properties: + numCPU: + description: | + Total number of vcpus in whole (i.e 1) of CPU pool. + type: integer + example: 1 + memory: + description: Total memory in mega bytes of CPU pool. + type: integer + example: 1024 + topology: + type: object + description: | + CPU pool topology defines an application's CPU-based + architecture. + When deploying for high availability or redundancy, it + allows for clustering with a configurable number of nodes + and minimum CPU/memory resource per Kubernetes node + requirements. + required: + - minNumberOfNodes + - minNodeCpu + - minNodeMemory + properties: + minNumberOfNodes: + description: | + Minimum number of worker nodes required by the + application. + type: integer + example: 5 + minNodeCpu: + description: | + Minimum number of vcpus in whole (i.e 1) per cluster + node in CPU pool. + type: integer + example: 2 + minNodeMemory: + description: | + Minimum memory in mega bytes per cluster node in + CPU pool. + type: integer + example: 1024 + gpuPool: + required: + - numCPU + - memory + - gpuMemory + - topology + type: object + description: | + GPU Pool refers to the amount of resources of the application + that is executed in nodes with GPU. + GPU Pool is not mandatory when the application is executed + exclusively in a CPU pool. + A GPU pool is composed by memory, CPU and GPU memory + properties: + numCPU: + description: | + Total Number of vcpus in whole (i.e 1) of GPU pool. + type: integer + example: 1 + memory: + description: Total memory in mega bytes of GPU pool. + type: integer + example: 1024 + gpuMemory: + description: Total GPU memory in giga bytes of GPU pool. + type: integer + example: 16 + topology: + type: object + description: | + GPU pool topology defines an application's GPU-based + architecture. + When deploying for high availability or redundancy, it + allows for clustering with a configurable number of nodes + and minimum CPU/memory/GPU memory resource per Kubernetes + node requirements. + required: + - minNumberOfNodes + - minNodeCpu + - minNodeMemory + - minNodeGpuMemory + properties: + minNumberOfNodes: + description: | + Minimum number of worker nodes with GPU required by + the application. + type: integer + example: 2 + minNodeCpu: + description: | + Minimum number of vcpus in whole (i.e 1) per cluster + node in GPU pool. + type: integer + example: 2 + minNodeMemory: + description: | + Minimum memory in mega bytes per cluster node in + GPU pool. + type: integer + example: 1024 + minNodeGpuMemory: + description: Minimum memory in giga bytes per cluster + node in GPU pool. + type: integer + example: 8 + isStandalone: + description: | + Define if the Kubernetes clusters can be reused by other + applications. + type: boolean + example: false + version: + type: string + description: Minimum Kubernetes Version. + example: "1.29" + additionalStorage: + type: string + description: | + Amount of persistent storage allocated to the Kubernetes PVC. + example: 80GB + pattern: ^\d+(GB|MB)$ + networking: + $ref: '#/components/schemas/K8sNetworking' + addons: + $ref: '#/components/schemas/K8sAddons' + + VmResources: + description: Definition of Virtual Machine Infrastructure + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: virtualMachine + enum: + - virtualMachine + numCPU: + type: integer + description: | + Number of vcpus in whole (i.e 1) + example: 1 + memory: + type: integer + example: 1024 + description: Memory in mega bytes + additionalStorages: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + DockerComposeResources: + description: Definition of Docker Compose Infrastructure + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: dockerCompose + enum: + - dockerCompose + numCPU: + type: integer + description: | + Number of vcpus in whole (i.e 1) + example: 1 + memory: + type: integer + example: 1024 + description: Memory in mega bytes + storage: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + ContainerResources: + description: Container Infrastructure Definition + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: container + enum: + - container + numCPU: + $ref: '#/components/schemas/Vcpu' + memory: + type: integer + example: 1024 + description: Memory in mega bytes + storage: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + Ipv4Addr: + type: string + format: ipv4 + example: "192.168.0.1" + description: | + IP of the device. A single IPv4 address may be specified in + dotted-quad form 1.2.3.4. Only this exact IP number will match the flow + control rule. + + Ipv6Addr: + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IP of the device. A single IPv6 address, following IETF 5952 + format, may be specified like 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + OperatingSystem: + description: | + Information about the Operating System of the application image + type: object + required: + - architecture + - family + - version + - license + properties: + architecture: + description: Type of the OS Architecture + type: string + enum: + - x86_64 + - x86 + example: x86_64 + family: + description: Family to which OS belongs + type: string + enum: + - RHEL + - UBUNTU + - COREOS + - WINDOWS + - OTHER + version: + description: Version of the OS + type: string + enum: + - OS_VERSION_UBUNTU_2204_LTS + - OS_VERSION_RHEL_8 + - OS_MS_WINDOWS_2022 + - OTHER + license: + description: License needed to activate the OS + type: string + enum: + - OS_LICENSE_TYPE_FREE + - OS_LICENSE_TYPE_ON_DEMAND + - OTHER + + Port: + type: integer + description: Port to stablish the connection + minimum: 0 + + RequiredResources: + description: | + Fundamental hardware requirements to be provisioned by the + Application Provider. + oneOf: + - $ref: "#/components/schemas/KubernetesResources" + - $ref: "#/components/schemas/VmResources" + - $ref: "#/components/schemas/ContainerResources" + - $ref: "#/components/schemas/DockerComposeResources" + discriminator: + propertyName: infraKind + mapping: + kubernetes: "#/components/schemas/KubernetesResources" + virtualMachine: "#/components/schemas/VmResources" + container: "#/components/schemas/ContainerResources" + dockerCompose: "#/components/schemas/DockerComposeResources" + + SubmittedApp: + description: Information about the submitted app + type: object + properties: + appId: + $ref: '#/components/schemas/AppId' + + Uri: + type: string + example: https://charts.bitnami.com/bitnami/helm/example-chart:0.1.0 + description: | + A Uniform Resource Identifier (URI) as per RFC 3986, + identifies the endpoint within an Edge Cloud Zone where the user + equipment may connect to the selected application instance + + responses: + '400': + description: Bad request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + message: "Schema validation failed at ..." + '401': + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + message: "Authorization failed: ..." + '403': + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + '404': + description: Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + message: "Resource does not exist" + '410': + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 410 + code: GONE + message: "The resource has been permanently removed" + '500': + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + message: "Internal server error: ..." + '501': + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 501 + code: NOT_IMPLEMENTED + message: "Service not implemented" + '503': + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" +``` diff --git a/marked/EdgeCloud/documentation/API_documentation/README/raw.md b/marked/EdgeCloud/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7ddb76c5e0e34810fef83d541ae441203a16f369 --- /dev/null +++ b/marked/EdgeCloud/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This document should be deleted upon addition of any file in this folder. diff --git a/marked/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story/raw.md b/marked/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6972616e634dac0aee65c2916d16e5f526966a41 --- /dev/null +++ b/marked/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story/raw.md @@ -0,0 +1,83 @@ + +Edge Application Management User Story +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)_ +_Roles are referenced from the ITU-T Cloud Refence Architecture._ + +## Summary +"As an Application Developer, I want to determine the Edge Cloud Zone more suitable for my application, being aware of all the options available their status and region of interest. +I want to be able to put my application available in the selected Edge Cloud Zone or Region in a simpler manner providing both artifacts and metadata for instantiating my application succesfully at the same time I want to be able to terminate +running instances of my application on a particular Edge Zone or Region and also to remove information of the whole application itself ". + +This story includes the whole journey from discovering Edge Cloud Zones available to run instances of the application and terminate them : + + +## Actors, Roles, and Scope +| Actor | Role | Scope | +|-------|------|-------| +|Application Provider (AP) |API Consumer | API requester | +|Operator Platform (OP)|Edge Cloud Provider | API Publisher | +|Edge Infrastructure Provider (EIP)|Edge Cloud Provider| + +Note the role of Edge Cloud Provider may be played by either the Operator or a Hyperscaler. + +## Pre-conditions +The AP has a resource usage agreement with the Operator Platform + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Network operators offers a Multi-access Edge Computing platform in a given territory with several levels of abstraction being the Edge Cloud Zone the lowest one. Network operators offers a service through EdgeCloud APIs that permits application providers to deploy instances of an application in one or several Edge Cloud Zones, and to Applications Users the posibility to chose the most appropriate Edge Cloud Zone available at a given moment| M | +|Pre-conditions|The AP has a resource usage agreement with the Operator Platform| M | +|Begins when|The Application Provider (AP) invokes the EdgeCloud API to submit at application with references to obtain all needed data for their instantiation (container images or VM images and manifests describing required resources by an application)| M | +|Step 1|The OP authorizes the request (terminates with a notification to the AP if it is not valid)| M | +|Step 2|The OP validates the request (terminates with a notification to the AP if content is not valid)| M| +|Step 3|The OP stores the app information and returns an Id for reference (terminates with a notification to the AP if error)| M | +|Step 4|The OP request information of currently available Edge Cloud Zones and Regions and their status| M | +|Step 4|The AP invokes the EdgeCloud API to instantiate the application in a given Region, it can also include an specific Edge Cloud Zone referencing previously generated appId | M | +|Step 5|The OP validates the request and if AppId and parameters provided are valid, returns an object including references to one instance Id per Edge Cloud Zone with an instantiation status "instantiating" and starts deploying app instance in EdgeCloud Zones that meet the input criteria| M | +|Step 6|The AP may request updated information of existing app instances of a given app. Possible status for app instantiation includes "ready" also information for endpoint info is provided for the app instance| O | +|Step 7|App instance may provide service for end users | O | +|Step 8|The AP request termination of one app instance (optionally all app instances in a given region) | M | +|Step 8|The OP validates the request (terminates with a notification to the UE if content is not valid e.g. given appId does not exist)| M| +|Step 9|The OP response to the AP and starts the termination of the app instance, moving its status to terminating| M| +|Step 10|The UE connects to the provided EAS and start using the application| M| +|Ends when|The UE connects to the EAS| M | +|Post-conditions|The UE is connected to the most adequate EAS, it may request to reconnect (repeat Step 10) at any time if the perceived quality is not adequate| M | +|Exceptions|
                        • During the step 2 the , the OP can not be able to download the image
                        • During the step 5 the Edge cloud zone resources are not available | M | + + + +## Flow +```mermaid +sequenceDiagram + participant AP + participant OP + participant EIP + Note over AP,OP: PRE App on device attached
                          to operator network + Note over AP,OP: PRE App developer registered,
                          authenticated and authorised + AP->>OP: GET /edge-cloud-zone + OP->>AP: Returns the information about the Edge cloud zones (edgeCloudZoneInfo) + alt app has a local mapping of server endpoints to Edge Cloud Zones + AP->>OP: POST /app Information about app to be instantiate(appManifest) + OP->>AP: Returns the identificator of the submitted app (appId) + AP->>OP: GET /app?appId=UUID Information about app(appId) to be instantiate(appManifest) + OP->>AP: Returns the information requested (appManifest) + AP->>OP: DELETE /app (appId) Delete app for a given appId (Manifest and any related information) + OP->>AP: Request accepted + AP->>OP:POST /app Instantiate application (appId) in a determinated Edge Cloud Zone(edgeCloudZoneId) + OP->>EIP: Instantiate instance in a determinated Edge Cloud Zone(edgeCloudZoneId) + EIP->>OP: Application instantiated + OP->>AP:Returns the appInstance created + AP->>OP: GET /app (appId) /Instance?appID=UUID Information about app(appId) instantiated (appInstanceInfo) + OP->>AP: Returns the application instance information + AP->>OP: DELETE /app (appId) DELETE Running instance for a given appId. + alt delete only the instance related with the appId + OP->>EIP: Delete instance + EIP->>OP: Instance deleted + OP->>AP: Application instance deleted + end + end +``` + + + + diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f25734744d5e5f7b4fd641c963321fa1d64c94dc --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816/raw.md @@ -0,0 +1,36 @@ +# MOM - 2020816 + +**Date:** 16-July-2022 + +## Attendees + +* Andrew Wajs (Scenera) +* Christoph Neumann (Broadpeak) +* Alexandru Ciinaru (Orange) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Landon Cox (MSFT) +* Mark Cornall (GSMA) +* Toshiyasu Wakayama (KDDI) +* Jesse Bijl – (EdgeXR) +* Thomas Vits – (EdgeXR) +* Jon Gainsley – (EdgeXR) +* Mahesh Chapalamadugu – (5GFF) +* Raghuram Parvataneni - (5GFF) +* Syed Rehman – (5GFF) +* Kevin Smith (5GFF) +* Urvika +* David Ferreira Antoniello (TEF) +* Aurelia Martinez Guerra (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| EdgeXR API proposal | EdgeXR | EdgeXR generated 2 API pull requests for thisgroup: *App APIs* [#26](https://github.com/camaraproject/EdgeCloud/pull/26) and *App session and Discovery APIs* [#27](https://github.com/camaraproject/EdgeCloud/pull/27). Jon Gainsley made a general overview of each one. During the session, the possibility of sharing the call flow or sequence diagram of the APIs was requested. EdgeXR will fetch this information and share it. | +| Comment - Pull Request [#21](https://github.com/camaraproject/EdgeCloud/pull/21) | 5GFF | [#21](https://github.com/camaraproject/EdgeCloud/pull/26) - Create EdgeCloudApi\_v0.0.5. yaml: Added a list of API questions today in the pull request. An additional specific session is proposed to discuss the points and questions. It was asked who would be interested in participating, the invitation will be sent to all participants. | +| Comment - Pull Request [#24](https://github.com/camaraproject/EdgeCloud/pull/24) | 5GFF | [#24 - UNI API](https://github.com/camaraproject/EdgeCloud/pull/26): Comments from 5GFF about removing or not the UNI API in this CAMERA group. Mahesh gives first feedback indicating that it will not be very easy for non-Telco users to use the API. This argument is complemented with additional points in the pull request. On the part of Telefonica, it is internally evaluating to have an answer as soon as possible. If necessary, a specific session can be established to discuss this point. Kevin explained that the term 'UNI' is specifically defined in public GSMA materials as requiring a client SDK/middleware ('User Client') on the client UE; and that 5GFF does not require that User Client. 5GFF API allows an application in the UE to call HTTP(S) operator-hosted APIs directly without requiring any additional SDK to be on the UE. | +| Draft Proposal for contributions and approval process in WG - Pull request by DT - [#20](https://github.com/camaraproject/EdgeCloud/pull/26) | DT | It is proposed to work with different subbranches. During the last two weeks, no comments have been received on what was proposed by DT, so it is assumed that all the members of this group agree with this proposal. The next step will be to move the 5GFF contribution to a sub-branch and work on different branches in order to push the proposal to the master branch for approval. In parallel, the way to work to validate the 3 current proposals (MEC Contribution, 5GFF Contribution and EdgeXR Contribution) will be having technical meetings to discuss each point and have the final decision. EdgeXR is interested in managing and organizing these activities. The proposal is that Thomas Vits prepare and elaborate a first proposal for the next technical meeting during the next 2 weeks and have a status in the next bi-weekly session. Different technical activities will be worked on in parallel. | +| Next steps | EdgeXR & TEF | Telefonica and EdgeXR will discuss the next steps to follow will be discussed, beginning with the analysis with the superposition of each proposal and, as a second step, defining the Action Points to have the Edge Cloud API family with all the required functionalities, the discussion of adding or not the UNI API to the Edge Cloud API family | diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f15a18c2f547f73b10cdf6f4d0f69e824783b4ef --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719/raw.md @@ -0,0 +1,43 @@ +## APMeting Information + +**Date:** 19-July-2022 + +## Attendees + +* +* Andrew Wajs (Scenera) +* Babu Narayan (Nabstract) +* Christoph Neumann (Broadpeak) +* Alexandru Ciinaru (Orange) +* Tuan Tran (Broadpeak) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Kevin Smith (5GFF) +* Larry Homer  (Intel) +* Landon Cox (MSFT) +* Sylvain Morel (Orange) +* Raffaele Passannanti (TIM) +* Fabrizio Moggio (TIM) +* Tom van Pelt (GSMA) +* Toshiyasu Wakayama (KDDI) +* Yamina Kelm (DT) +* Shilpa Padgaonkar (DT) +* Eric Murray (Vodafone) +* Jesse Bijl +* Thomas Vits +* Aurelia Martinez Guerra (TEF) +* David Ferreira Antoniello (TEF) +* Cristina Santana (TEF) +* José Antonio Ordoñez (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| API Deployment | Capgemini & TEF | TheYAML Swagger associated with the APIs proposed and created by  Orange, DT,Capgemini and Telefonica was presented and detailed. It is the initial ideathat is presented as a starting point to be complemented, edited and reviewedby the participants.  | +| Edge API Family proposal | Capgemini & TEF | An analysis realizedby Telefonica associated with the 5GFF APIs and the Deployment APIs, and thepossible relationship between them, was presented. 
                          https://github.com/camaraproject/EdgeCloud/blob/main/documentation/Presentation/EdgeXR\_forCAMARAEdgeCloudWG\_20220719.pdf | +| EdgeXR Presentation | EdgeXR | Thomas Vitsintroduces EdgeXR and indicates that they want to support and be part of thedevelopment of the CAMARA APIs, taking advantage of the experience gainedduring the MobiledgeX stage. The presentation is included. 
                          https://github.com/camaraproject/EdgeCloud/blob/main/documentation/Presentation/EdgeXR\_forCAMARAEdgeCloudWG\_20220719.pdf | +| | | | +| | | | diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e1b33eba91e69e3bb58be635a54f1b5bae2376f9 --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802/raw.md @@ -0,0 +1,41 @@ +## AP Meting Information + +Date: 02 –August - 2022 + +## Attendees + +* Andrew Wajs (Scenera) +* Alexandru Ciinaru (Orange) +* Tuan Tran (Broadpeak) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Larry Homer (Intel) +* Tom van Pelt (GSMA) +* Toshiyasu Wakayama (KDDI) +* Yamina Kelm (DT) +* Shilpa Padgaonkar (DT) +* Thomas Vits (EdgeXR) +* Emil Zhang +* Kevin Xu +* Mahesh Chapalamadugu (5GFF) +* Mark Cornall (GSMA) +* Urvika +* Larry Horner (Intel) +* Vaibhav Mehta (Nabstract) +* Alexandre Harmand (TEF) +* David Ferreira Antoniello (TEF) +* Aurelia Martinez Guerra (TEF + +
                          +
                          +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| #21 API Deployment | Capgemini & TEF | Telefónica in collaboration with Capgemini, uploaded to GitHub as a “pull request” the Edge Deployment API (EdgeCloudApi\_v0.0.5.yaml - [https://github.com/camaraproject/EdgeCloud/pull/21](https://github.com/camaraproject/EdgeCloud/pull/21) 
                          In this YAML it includes the 4 APIs proposed in the first meeting:
                          • Application Artifacts Management
                          • Application Provider Resource Management
                          • Application Onboarding Management
                          • o Application Instance Lifecycle Management
                          Participants can review it and give any additional comments. | +| Edge API Family proposal | EdgeXR | The objective of Telefonica and Capgemini was to have for this meeting a first proposal about the analysis of the parameters to join the 5GFF APIs (Discovery) with the new APIs that were uploaded today (focused on the deployment of the APIs). It was not possible to have it for this week. Two options are proposed:
                          1. Telefonica continues to prepare this new proposal and share it at the next meeting, starting technical activities in parallel to discuss this proposal.
                          2. Another candidate from the group who can collaborate in this analysis in order to have more people involved.
                          Thomas Vits (of EdgeXR) offers to collaborate with this point as another candidate. The objetive is to have a first proposal for the next meeting. | +| #20 Proposal for contributions and approval process in WG              | DT | DT has a "pull request" about the proposal for the Contribution and Approval process of this working group.
                          [https://github.com/camaraproject/EdgeCloud/pull/20](https://github.com/camaraproject/EdgeCloud/pull/20)

                          Shipa Padgaonkar presents the proposal located on the CAMARA GitHub.
                          It is important that everyone review and validate this proposal to make this way of working official.
                          This "pull request" will be maintained until Friday 08/12, if there are no additional comments, it will be validated.
                          It is important that everyone review and validate this proposal to make this way of working official. | +| #25 Draft proposalEdge Cloud GitHub repository Organization | Capgemini & TEF | Deepak,from Capgemini, in conjunction with Telefónica, presented a draft with 3 options for organizing the Edge Cloud GitHub repository. https://github.com/camaraproject/EdgeCloud/pull/25 Initially, during the meeting,some of the participants indicated that option 1 could be the most appropriate.In any case, the presentation is attached and, in case of having additionalcomments, it is established as a deadline to receive them until Friday 08/12. | +| #24 UNI API | Capgemini & TEF | Telefonica& Capgemini open a discussion about the Edge Cloud API Family scope. 
                          This EdgeCloud API Family must include the Edge Discover UNI API, or no? 
                          Telefonicaand Capgemini performed a first analysis of Pro and Cons.
                          Deepakpresented this first analysis. 
                          [https://github.com/camaraproject/EdgeCloud/pull/24](https://github.com/camaraproject/EdgeCloud/pull/24)
                          It isnecessary that the participants can establish if it is important for CAMARA todefine this UNI APIs or must be 3GPP.
                          Theproposal will remain open for the next two weeks, until the next meeting, toestablish a conclusion.. | diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..88506d26783ba9ba55124e578a01356eea96bd3e --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827/raw.md @@ -0,0 +1,40 @@ +# OM - 20220827 + +Sun, Sep 4, 2022 8:19 AM +
                          +## **Attendees** + +* Andrew Wajs – (Scenera) +* Christoph Neumann – (Broadpeak) +* Tim Epkes - +* Prashant Goswami – +* Deepak Gunjal – (Capgemini) +* Brett Hill – (Telstra - 5GFF) +* Kevin Smith – (Vodafone – 5GFF) +* Landon Cox – (MSFT) +* Mahesh Chapalamadugu - (Verizon – 5GFF) +* Sylvain Morel - (Orange) +* Fabrizio Moggio - (TIM) +* Raffaele Passannanti - (TIM) +* Raghuram Parvataneni - (Telstras – 5GFF) +* Syed Rehman - (Verizon – 5GFF) +* Thomas Vits - (EdgeXR) +* Tom van Pelt - (GSMA) +* Toshiyasu Wakayama (KDDI) +* Urvika +* Alexandre Harmand - (TEF) +* José Antonio Ordoñez - (TEF) +* David +* Ferreira Antoniello - (TEF) +* Aurelia Martínez Guerra - (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| CAMRA - Roles | TEF | Markus has defined the differentroles in each CAMARA group in order to be clear about which members will makenew contributions, which members will validate these contributions, etc. This activity has been developed in parallel during these last two weeks and has dedicated part of the time.
                          The toles are:
                          1. **Maintainers: A s**mall group which is acting as Sub Project Managers à listed in the MAINTAINERS.MD of theSub Project
                          2. **Codeowners**: A small group responsible for merging code / documents / PRs à listed in the CODEOWNERS of the SubProject (also technical readable file!)
                          3. Contributors:the whole community for a Sub Project able to contribute à listed as Contributors in GitHub (Markushas to invite, persons have to confirm).
                          | +| Edge Cloud API family | EdgeXR | Analysis of the different contributions to the API (5GFF, OPAG, EdgeX
                          R, New DT contribution). This activity is assigned to a new group in order to analyze all the contributions, define which APIs we must have in this Edge Cloud family, analyze the different APIs to align them with the proposal.
                          In the last session, the EdgeXR team was established as responsible for organizing this small group and starting the activities.
                          Thomas presented the next steps: Have a Kick-off meeting to start working on the activities. A link is attached for those who want to participate and indicate the best option according to availability: ([https://doodle.com/meeting/participate/id/dBLrAQna](https://doodle.com/meeting/participate/id/dBLrAQna)).
                          It is necessary to include in the analyzes of this group the pull request about the questions, doubts and comments of each proposal. For this, it is proposed as the first point on the agenda of the first session to resolve all doubts and questions. | +| ***Comment - Pull Request  #24*** | All | #24 - UNI API: There are different options for this API: Should this API be included in CAMERA? Should 3GPP be used to define this UNI API? Should a part of the API be defined in CAMERA and a part in 3GPP? It is proposed to start a small group to discuss this topic, align and share status in these bi-weekly sessions. It is important to fix this issue, whether or not UNI API is part of the Edge Cloud group, as soon as possible.
                          Deepak (Capgemini) is goin to arrange a short group that is going to have as objetive aligne possiions in this isue | +| Traffic Influence API | TIM | Fabrizio Moggio (TIM) opened a new discussion about the Traffic Influence API. He proposes to work on this API in EdgeCloug grou and that this new API be part og thi Edge Clud API family.

                          It was proposed to Fabrizio in the session that a point be opened in the Backlog group with all the details. This group will decide if it is better to create a new group in CAMARA specifically for Traffic Influence or if this functionality is part of one of the currently available groups. | \ No newline at end of file diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e41129213e0d255557ab22f38a2d89e8d2286ec7 --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160/raw.md @@ -0,0 +1,28 @@ +# Meeting Minutes Convergence Substream - 20220916 + +Fri, Sep 16, 2022 17:00 PM +
                          +## **Attendees** + +* Andrew Wajs(Scenera) +* Deepak Gunjal (Capgemini) +* Kevin Smith (Vodafone – 5GFF) +* Mahesh Chapalamadugu (Verizon - 5GFF) +* Syed Rehman (Verizon - 5GFF) +* Thomas Vits (EdgeXR) +* Lev Shvarts (EdgeXR) +* Alexandre Harmand (TEF) +* Rebecca Odenwaelder (Deutsche Telekom) +* Marc Cornall (GSMA) +* Alexandru Ciinaru (Orange) +* Toshiyasu Wakayama (KDDI) + +## Kickoff disucssion + +This call was to initiate the activity of the convergence substream. + +| Item | Who | Description | +| ---- | --- | ----------- | +| Substream Objectives and way of working| All | EdgeXR provided a suggestion on the objectives of this substream, below the aligned outcome after discussion
                          1. Situation: The EdgeCloud Project in CAMARA received already 3 API contributions (from 5GFF, Capgemini, EdgeXR) potentially addressing similar or same functionalities exposing edge cloud services
                          2. Challenge: (Assumption) The goal in CAMARA is to have single API set for a given developer intent (on a specific abstraction layer). <- This was a point of discussion whether that assumption actually holds true or whether different APIs could be feasible for the same intent. No final conclusion taken at this point.
                          3. Solution: Original proposal was to work on the assessment of the current/coming contributions but after discussion we concluded that the initial step to enable this would be to create an aligned taxonomy/terminology. This will ensure that we have the right vocabulary to actually do this assesment acknowledging that background of the distributions is diverse with having different taxonomy in mind.
                      | +| Logistics | All | 1. In order to be able to continue this substream despite of vacations etc. the group agreed to appoint Kevin (VDF/5GFF) as Co-Lead with Thomas (EdgeXR) for this substream.
                      2. Group agreed on a bi-weekly meeting cadence; as we have participants from literally all timezones we agreed to shift timeslots every 2 meetings to the next timzone (e.g. by around 8 hours)
                      3. Agreement that all discussions / documents shall be strictly happen in git| +| Establish aligned Taxonomy| All | As agreed in the initial disucssion the first step is to establish an aligned taxonomy. It was suggested to use the OPG definitions as a basis and then iterate on it in git to come to a consensus. Once good enough (to be agreed by the group when this milestone is hit) the next step (i.e. making an assesment of the scope of the different contributions using that taxonomy) can be initiated. Deepak, Thomas and Mahesh volunteered to get the intitial commit going. | diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b1b08b47063c1346500778d6b382adeefa9f2f2b --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023/raw.md @@ -0,0 +1,24 @@ +# Edgecloud - Meetings Minutes + +Meeting minutes are kept from December 2023 in https://wiki.camaraproject.org/display/CAM/Edge+Cloud, please refer to that page to follow last updates. + +## December 2023 + +12/12/2024 + +https://wiki.camaraproject.org/display/CAM/2023-12-12%3A+SP-EDC+Minutes + +19/12/2024 + +https://wiki.camaraproject.org/display/CAM/2023-12-19%3A+SP-EDC+Minutes + +## January 2024 + +09/01/2024 + +https://wiki.camaraproject.org/display/CAM/2024-01-09%3A+SP-EDC+Minutes + +23/01/2024 + +https://wiki.camaraproject.org/display/CAM/2024-01-23%3A+SP-EDC+Minutes + diff --git a/marked/EdgeCloud/documentation/MeetingMinutes/README/raw.md b/marked/EdgeCloud/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6819528982aec840a577b116c176f418ccfb8249 --- /dev/null +++ b/marked/EdgeCloud/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,5 @@ +# Minutes archive + +From December 2023 the meeting minutes of EdgeCloud calls are within the CAMARA Wiki at [https://wiki.camaraproject.org/display/CAM/Edge+Cloud](https://wiki.camaraproject.org/display/CAM/Edge+Cloud) + +Meeting minutes before December 2023 are here in the repository. diff --git a/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README/raw.md b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d4517609b5bc58d467d0f2af4d499e98b8a41b47 --- /dev/null +++ b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README/raw.md @@ -0,0 +1,3 @@ +# EdgeCloud – API\_Documentation +
                      +In this folder  will be all the documents about the Edge Cloud API Family \ No newline at end of file diff --git a/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story/raw.md b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..15b6925edce28713978947aa089cb0335ae81544 --- /dev/null +++ b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story/raw.md @@ -0,0 +1,60 @@ +## Actors, Roles, and Scope +| Actor | Role | Scope | +|-------|------|-------| +|Application Provider (AP) |API Consumer | API Requester | +|Edge Service Provider (ESP)|Edge Cloud Provider|API Publisher | +|MNO|Communications Service Provider|API Publisher | +|User Client(UC)|API Consumer|API Requester | + +Note: the role of Edge Service Provider may be played by different entities, for example: MNOs, Hyperscalers, etc + + + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Network operators offers a Multi-access Edge Computing platform in a given territory with several levels of abstraction being the Edge Cloud Zone the lowest one. Network operators offers a service through EdgeCloud APIs that permits application providers to deploy instances of an application in one or several Edge Cloud Zones, and to Applications Users the posibility to chose the most appropriate Edge Cloud Zone available at a given moment| M | +|Pre-conditions|The AP has a resource usage agreement with the Operator Platform| M | +|Begins when|The Application Provider (AP) invokes the Edge Application Management API to submit an application with references to obtain all needed data for their instantiation (container images or VM images and manifests describing required resources by an application)| M | +|Step 1|The ESP stores the app information and returns an Id for reference (terminates with a notification to the AP if error)| M | +|Step 2|The Application Provider (AP) request information of currently available Edge Cloud Zones and their status | M| +|Step 3|The MNO provides the availables Edge Cloud Zones where the AP could instantiate the Application| M | +|Step 4|The AP instantiates the application in one Edge Cloud Zone or in Severals| M| +|Step 5|The ESP response to the AP appInstance created| M | +|Step 6|The AP may request updated information of existing app instances of a given app. Possible status for app instantiation includes "ready" also information for endpoint info is provided for the app instance| O | +|Step 7|App instance may provide service for end users | O | +|Step 8|The AP request termination of one app instance (optionally all app instances in a given region) | M | +|Step 9|The ESP validates the request (terminates with a notification to the UE if content is not valid e.g. given appId does not exist)| M| +|Step 10|The ESP responds to the AP and starts the termination of the app instance, moving its status to terminating| M| +|Ends when|The UC connects to the EAS| M | + + + + +## Flow +```mermaid +sequenceDiagram + participant AP + participant MNO + participant ESP(Operator/Hyperscaler) + + Note over AP,MNO: PRE App on device attached
                      to operator network + Note over AP,MNO: PRE App developer registered,
                      authenticated and authorised + Note over MNO,MNO: Edge Application Management API + AP->>ESP(Operator/Hyperscaler): POST/ AP Invokes Edge Application Management API to submit an application with references to obtain all needed data for their instantiation(appManifest) + ESP(Operator/Hyperscaler)->>AP: The Operator stores the app information and returns an Id for reference(appId) + alt app has a local mapping of server endpoints to Edge Cloud Zones + AP->>MNO: GET/edge-cloud-zones AP request information about available Edge cloud zones + MNO->>AP: Returns the name of the available Edge cloud zones for the Application + AP->>ESP(Operator/Hyperscaler):POST/ The AP request to instantiate the App in one or several Edge Clod Zones(Deployment). + ESP(Operator/Hyperscaler)->>AP:Returns the appInstance created + AP->>MNO: GET /app (appId) Information about app(appId) instantiated + MNO->>AP: Returns the application instance information + AP->>MNO: DELETE /app (appId) DELETE Running instance for a given appId. + alt delete only the instance related with the appId + MNO->>ESP(Operator/Hyperscaler): Delete instance + ESP(Operator/Hyperscaler)->>MNO: Instance deleted + MNO->>AP: Application instance deleted + end + end +``` + diff --git a/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta/raw.md b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9bdf134d912e97ae783b3cba0c9b5c1200d7dd4a --- /dev/null +++ b/marked/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta/raw.md @@ -0,0 +1,12 @@ +# unotes_meta + +```json +{ + "name": "", + "isOrdered": true, + "folders": {}, + "files": { + "README": 0 + } +} +``` diff --git a/marked/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation/raw.md b/marked/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9d8dc5a06b81ce744e54f6bc4780d87b886361e7 --- /dev/null +++ b/marked/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation/raw.md @@ -0,0 +1,183 @@ +# Edge Cloud Intents and API Mapping – Harmonisation Document + +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) and references ITU-T Cloud Reference Architecture roles._ + +--- + +## 1. Summary + +This document provides a harmonised view of **EdgeCloud Intents** and their corresponding **CAMARA APIs**, consolidating the functional flow across discovery, deployment, runtime, and termination stages of the **Edge Cloud lifecycle**. + +The purpose is to bridge earlier MEC & Deployment API proposals with the current **CAMARA Edge Cloud family of APIs**, ensuring a unified lifecycle from **Zone discovery** to **Application endpoint registration and discovery**. + +--- + +## 2. Objectives + +- To define the **intents** supporting the lifecycle of Edge-hosted applications. +- To map these intents to existing and emerging **CAMARA APIs**. +- To support interoperability between **Operator Platforms** and **Application Providers**. +- To prepare the foundation for future harmonisation across **Edge, Application Management, and Network APIs** (e.g., Traffic Influence). + +--- + +## 3. Roles, Actors, and Scope + +| Actor | Role | Scope | +|-------|------|-------| +| Application Provider (AP) | API Consumer | API requester, deploys applications and manages instances. | +| Operator Platform (OP) | Edge Cloud Provider | API publisher, orchestrates resources and exposes APIs. | +| Edge Infrastructure Provider (EIP) | Edge Cloud Provider | Hosts and manages the physical/virtual infrastructure. | +| End User (UE) | Service Consumer | Interacts with applications hosted at the edge. | + +> Note: Edge Cloud Provider may be the Operator or a Hyperscaler. + +--- + +## 4. EdgeCloud Lifecycle Intents Overview + +| **Intent ID** | **Intent Name** | **Purpose / Description** | **Mapped CAMARA API / Status** | +|---------------|----------------|----------------------------|--------------------------------| +| **Intent 1** | Discover EdgeCloud Zones | Discover the closest Edge Cloud Zone to a user device based purely on network topology (shortest network path). | `Simple Edge Discovery API` | +| **Intent 2** | List Available Regions / Capabilities | Discover the best Edge Cloud Zone for an application, considering compute, storage, and network performance requirements beyond distance. | Planned extension of Optimal Edge Discovery | +| **Intent 3** | Retrieve Zone Information | Obtain metadata, KPIs, and current resource availability of a specific Edge Cloud Zone. | `Simple Edge Discovery API` | +| **Intent 4** | Filter / Select Preferred Zones | Apply filters (latency, region) for optimal zone selection. | Planned enhancement within Optimal Edge Discovery | +| **Intent 5** | Register / Onboard Application | Upload manifests, metadata, and container images. | `Edge Cloud Lifecycle Management API` | +| **Intent 6** | Validate Application Metadata | Validate manifests and dependencies before deployment. | Partially covered by Lifecycle Management | +| **Intent 7** | Instantiate Application | Deploy application instances in selected Edge Zones. | `Edge Cloud Lifecycle Management API` | +| **Intent 8** | Scale Application Instance | Adjust resources dynamically (horizontal/vertical). | Future – EdgeCloud Scaling API (proposed) | +| **Intent 9** | Register Application Endpoints | Register deployed app endpoints (URLs, ports, zones). | `Application Endpoint Registration API` | +| **Intent 10** | Update Endpoint Metadata | Modify endpoint details (status, performance). | Within `Application Endpoint Registration API` | +| **Intent 11** | Discover Optimal Application Endpoints | Find best endpoint for a device based on latency or policy. | `Application Endpoint Discovery API` | +| **Intent 12** | Client-Side Endpoint Selection | Allow clients to select among multiple available endpoints. | Optional behaviour of Endpoint Discovery | +| **Intent 13** | Influence Network Traffic | Apply routing rules for premium users or optimisation. | `Traffic Influence API` | +| **Intent 14** | Configure Network Policies | Manage slicing/routing preferences for traffic flows. | Evolution of Traffic Influence | +| **Intent 15** | Monitor Application Performance | Retrieve runtime telemetry: latency, usage, etc. | SessionInsights API | +| **Intent 16** | Retrieve Edge Metrics / Zone Health | Query Edge Zone health and operational metrics. | Under discussion – EdgeCloud Monitoring API | +| **Intent 17** | Automate Policy or Scaling Actions | Enable closed-loop orchestration and scaling triggers. | Future – Edge Orchestration Intent API | +| **Intent 18** | Terminate Application | Decommission instances and release resources. | `Edge Cloud Lifecycle Management API` | +| **Intent 19** | Deregister Application Endpoints | Remove obsolete endpoints from registry. | `Application Endpoint Registration API` | +| **Intent 20** | Audit and Logging | Track API operations, logs, and service usage. | Commonalities Cross-API Logging proposal | +| **Intent 21** | Federated Edge Discovery | Discover edge zones from partner operators/hyperscalers. | Proposed – Edge Federation Discovery API | +| **Intent 22** | Cross-Operator Application Placement | Deploy app instances across federated networks. | Future CAMARA/GSMA initiative | +| **Intent 23** | Consent and Policy Management | Manage end-user consent during discovery/exposure. | Privacy & Consent WG | +| **Intent 24** | Service Quality Enforcement | Apply QoS constraints dynamically per application. | Future – Edge QoS Policy API | +| **Intent 25** | Edge Resource Reservation / Pre-Booking | Reserve compute/storage/network capacity pre-deployment. | Proposed – Edge Reservation API | + +--- + + +## 5. Harmonised EdgeCloud Lifecycle Flow + +```mermaid +flowchart LR + A[Intent 1: Discover Edge Zones] --> B[Intent 3: Retrieve Zone Info] + B --> C[Intent 5: Register Application] + C --> D[Intent 7: Instantiate Application] + D --> E[Intent 9: Register Application Endpoints] + E --> F[Intent 11: Discover Optimal Endpoints] + F --> G[Intent 13: Apply Traffic Influence - optional] + G --> H[Intent 18: Terminate Application] +``` +```mermaid +sequenceDiagram + participant AP as Application Provider + participant OP as Operator Platform + participant EIP as Edge Infrastructure Provider + participant UE as User Equipment + participant AF as Application Function + + Note over AP,OP: Phase 1 - Discovery + AP->>OP: POST /discover-optimal-edge-zones + OP-->>AP: EdgeCloudZone list ordered by proximity + + Note over AP,OP: Phase 2 - Provisioning & Deployment + AP->>OP: POST /applications (Onboard Application) + OP-->>AP: Returns appId + AP->>OP: POST /applications/{appId}/instances + OP->>EIP: Instantiate app in target Edge Zone + EIP-->>OP: Instance ready + OP-->>AP: appInstanceId + status "RUNNING" + + Note over AP,OP: Phase 3 - Endpoint Management + AP->>OP: POST /register (Application Endpoint) + OP-->>AP: endpointId confirmation + + Note over UE,OP: Phase 4 - Runtime & Discovery + UE->>OP: POST /retrieve-optimal-app-endpoints {appId, device} + OP-->>UE: Returns optimal endpoint (EdgeCloudZoneId, endpointURL) + + Note over AF,OP: Phase 5 - Network Optimisation + AF->>OP: POST /traffic-influence (toward EAS) + OP-->>AF: Returns routing configuration ID + UE->>EIP: Connect to optimal EAS endpoint +``` +# CAMARA EdgeCloud Harmonisation Analysis + +## 7. Harmonisation Analysis + +### 7.1 API Relationship Summary + +- **Simple Edge Discovery**: Provides baseline nearest-zone discovery using network proximity. +- **Optimal Edge Discovery**: Extends discovery with richer metadata (zone characteristics, latency, region). +- **Edge Application Management**: Enables deployment and lifecycle control of applications in these zones. +- **Application Endpoint Registration**: Establishes registry of deployed endpoints. +- **Application Endpoint Discovery**: Allows clients or servers to dynamically retrieve optimal endpoints. +- **Traffic Influence**: Complements discovery and lifecycle by providing routing enforcement at the network level. + +### 7.2 Common Design Principles + +- **Entity Alignment**: Shared objects (e.g., `edgeCloudZoneId`, `appId`, `endpointId`) across all APIs. +- **Security Consistency**: All APIs assume OAuth2-based access with clear roles. +- **Consent Integration**: Optional per API (explicit in Discovery and Endpoint APIs). +- **Operator Neutrality**: APIs work across multiple operators via federated exposure models. + +**Conclusion**: CAMARA EdgeCloud APIs collectively address all intents from earlier MEC proposals, forming a continuous lifecycle from discovery → provisioning → runtime → termination. + +## 8. Harmonised Data Model Overview + +| Entity | Description | Referenced In | +|--------|-------------|---------------| +| `edgeCloudZoneId` | Identifier of Edge Cloud Zone | Discovery, Lifecycle, Endpoint APIs | +| `appId` | Unique application identifier | Lifecycle, Endpoint Discovery | +| `appInstanceId` | Deployed instance ID | Lifecycle API | +| `endpointId` | Registered endpoint for a deployed instance | Endpoint Registration & Discovery | +| `deviceId` | Device identifier or token | Discovery and Endpoint Discovery APIs | +| `trafficInfluenceId` | Identifier for a network routing session | Traffic Influence API | + +## 9. Inter-API Dependencies + +| API | Depends On | Dependency Description | +|-----|------------|------------------------| +| Simple Edge Discovery | None | Can be used standalone for planning | +| Optimal Edge Discovery | None | Can be used standalone for planning | +| Edge Application Management | Optimal Edge Discovery | Uses discovered zones for deployment decisions | +| Application Endpoint Registration | Edge Cloud Lifecycle Management | Registers endpoints of instantiated applications | +| Application Endpoint Discovery | Endpoint Registration | Discovers registered endpoints | +| Traffic Influence | Endpoint Discovery | Optimises routing to discovered endpoints | + +**Harmonised APIs together enable a complete closed loop**: +Discovery → Deployment → Registration → Discovery (endpoint) → Influence → Termination. + +## 10. Open Harmonisation Topics + +| Area | Description | Next Step | +|------|-------------|-----------| +| Unified Discovery Schema | Align Simple and Optimal Edge Discovery response objects | Define a shared `EdgeCloudZoneInfo` schema | +| Cross-API Security Scopes | Establish unified OAuth2 roles and scopes | Coordinate with Commonalities WG | +| Consent Management | Define consistent consent-handling process across Discovery and Endpoint APIs | Align with Privacy & Consent WG | +| Federated Operations | Support discovery and lifecycle across multi-operator environments | Introduce Edge Federation API concept | +| Traffic Policy Automation | Enable dynamic network steering based on real-time metrics | Collaborate with Network API group | + +## 11. References + +- **CAMARA – Simple Edge Discovery API**: [User Story](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/main/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md) +- **CAMARA – Optimal Edge Discovery API**: [User Story](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/main/documentation/API_documentation/optimal-edge-discovery-User-Story.md) +- **CAMARA – Edge Application Management**: [User Story](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/API_Documentation/User%20Stories/Edge.Cloud.Lifecycle.Management.User.Story.md) +- **CAMARA – Application Endpoint Registration API**: [User Story](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/main/documentation/API_documentation/application-endpoint-registration-User-Story.md) +- **CAMARA – Application Endpoint Discovery API**: [User Story](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/main/documentation/SupportingDocuments/API_Documentation/User%20Stories/Application%20Endpoint%20Discovery%20User%20Story.md) +- **CAMARA – Traffic Influence API**: [User Story](https://github.com/camaraproject/TrafficInfluence/blob/main/documentation/API_documentation/traffic-influence-user-story-use-case-1.md) +- **GSMA – Open Gateway & CAMARA Harmonisation Framework**: [Reference](https://www.hcltech.com/sites/default/files/documents/resources/whitepaper/files/2024/09/16/gsma-open-gateway.pdf?utm_source=chatgpt.com) + + + diff --git a/marked/EdgeCloud/documentation/SupportingDocuments/README/raw.md b/marked/EdgeCloud/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/EdgeCloud/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/EnergyFootprintNotification/README/raw.md b/marked/EnergyFootprintNotification/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0e263dab5efe77ccc89d08f2a31c389f30911864 --- /dev/null +++ b/marked/EnergyFootprintNotification/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# EnergyFootprintNotification + +Sandbox API Repository to describe, develop, document, and test the EnergyFootprintNotification Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/aoDJAw) +* [Provider Implementation](https://github.com/camaraproject/EnergyFootprintNotification_PI) + +## Scope + +* Service API(s) “EnergyFootprintNotification” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API(s) provide(s) the customer with the ability to: + * Retrieve the information about the E2E energy consumption and Carbon Footprint for a specified service that is provided by a certain number of active instances of an application. The applications that are monitored for their energy consumption are the ones managed by the operator and that run on top of the operator’s infrastructure. For example the application managed with the [CAMARA Edge Cloud APIs](https://github.com/camaraproject/EdgeCloud). +* Describe, develop, document, and test the API(s) +* Started: January 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/EnergyFootprintNotification/releases/tag/r1.3) (Fall25), with the following API versions: + * **energy-footprint-notification v0.1.0** + [[YAML]](https://github.com/camaraproject/EnergyFootprintNotification/blob/r1.3/code/API_definitions/energy-footprint-notification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/EnergyFootprintNotification/r1.3/code/API_definitions/energy-footprint-notification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/EnergyFootprintNotification/r1.3/code/API_definitions/energy-footprint-notification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/EnergyFootprintNotification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/EnergyFootprintNotification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/EnergyFootprintNotification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly, Tuesday 13:00 – 14:00 UCT + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99704469014?password=31affe33-8c78-42f3-9cec-32efee113700) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/67076164) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list https://lists.camaraproject.org/g/sp-efn. + * A message to the community of this Sub Project can be sent using sp-efn@lists.camaraproject.org. diff --git a/marked/EnergyFootprintNotification/code/API_definitions/README/raw.md b/marked/EnergyFootprintNotification/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/EnergyFootprintNotification/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification/raw.md b/marked/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c5bb04687faf4b159cc9e041efa93179d7631389 --- /dev/null +++ b/marked/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification/raw.md @@ -0,0 +1,1043 @@ +# energy-footprint-notification + +```yaml +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Energy Footprint Notification + description: | + ## Overview + The Energy Footprint Notification API provides the API Consumer + with information about the energy consumption and carbon footprint of a + service exposed by a set of applications instances. + ## Introduction + The scenario foresees a service provided by many applications, the Energy + Footprint API provides the API Consumer (e.g. the Service Provider) + with the information about the energy consumption and carbon + footprint (greenhouse gases emissions) of the service produced by the + active applications instances hosted by the Telco Operator. + Note: This API is expected to be used in conjunction with, for example, + the CAMARA Edge Cloud APIs. + + **Example use case and flow:** + + [**Edge Service energy report**](https://github.com/camaraproject/EnergyFootprintNotification/blob/r1.3/documentation/API_documentation/EFN_UserStory_UseCase_1.md) + + ## API Documentation + ## Details + The Energy Footprint Notification API provides, to the API Consumer, + information about the energy consumption and carbon footprint for a + specified service that is provided by a certain number of active instances + of some applications. The API provides information about the aggregated + energy consumption and carbon footprint considering all the active instances + and network involvement, in a specific time period in which the service is + provided to end users. The application instances that are monitored + for their energy consumption are the one managed by the Operator and that + run on top of the Operator’s infrastructure. The service is deployed and + managed via the Operator Platform (e.g via the [CAMARA Edge Cloud APIs](htt\ + ps://github.com/camaraproject/EdgeCloud)). Consequently, the Operator + Platform is aware of all the active instances supporting the service and it + is also aware of the energy consumption in the Data Centers hosting the + applications instances providing the service. The Operator's Network is + deeply involved in the service provisioning, so its energy consumption is + relevant to have and view. The Energy Footprint Notification API also considers the energy + consumption and the carbon footprint for the network traffic generated by + the Operator's subscribers consuming the service. The Service Provider + activates a service using the Operator Platform to instantiate and activate + the application supporting the service in different Edge Data Centers. + The Service Provider onboards the applications, deploys and activates some + instances to enable the service. Service customers use their devices to + access the service. The use of the service produces an energy + consumption alongside the Operator's Network and on the Data Centers hosting + the applications instances. The Energy Footprint Notification API is used by a Service Provider to be + aware of the energy consumption of the service. The Service Provider, + via an Energy Footprint Notification API Consumer, invokes the Energy Footprint Notification API with the identifiers of the + application instances supporting the target service. A period of + time can be specified; it must start after the API subscription and can be limited. + The Energy Footprint Notification API provides back the energy consumption by + the service in that period of time. The Energy Footprint Notification API also provides back the + carbon footprint related to the running of the service. + The Energy Footprint Notification API is an intent based API. + + The Energy Footprint Notification API supports the following Intents: + - Intent1: Which is the overall energy consumption for my service in this + period of time? + - Intent2: Which is the overall carbon footprint for my service in this + period of time? + + The input for the above intents is: + - Input_Intent1: Set of applications identifiers and period of time. + - Input_Intent2: Set of applications identifiers and period of time. + + The output for the above intents is: + - Output_Intent1: energy consumption in Kw/h. + - Output_Intent2: greenhouse gases emission in tonnes. + + The related endpoints are: + - Intent1: /calculate-energy-consumption + - Intent2: /calculate-carbon-footprint + + **The main elements of the Energy Footprint Notification API are:** + + **ReportCreationRequest:** + Information about the target service (as a + set of applications) and the period of time of interest. + The period must start after the API subscription and can be limited. + It includes the parameter "service" which is an array of application + identifiers. The application identifiers are provided by the CAMARA API + used to deploy the applications (e.g. the Edge Application Management API). + + **EnergyResponse:** + Provides to the API Consumer the requested information about the energy + consumption for the target service, considering all the active instances, + in the period of time of interest. + + **CarbonFootprintResponse:** + Provides to the API Consumer the information about the carbon footprint for + the target service, considering all the active instances, in the period of + time of interest. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/EnergyFootprintNotification +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/energy-footprint-notification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. + `api.example.com` or `api.example.com/somepath` +security: + - notificationsBearerAuth: [] +############################################################################ +# Tags # +############################################################################ +tags: + - name: Energy consumption information retrieval + description: Request information on the energy consumption of the service. + - name: Carbon footprint information retrieval + description: Request information on the carbon footprint for the service. +############################################################################ +# Paths # +############################################################################ +paths: + /calculate-energy-consumption: + post: + tags: + - Energy consumption information retrieval + summary: Provides the overall Energy Consumption for the target + Application instances in a certain period of time. + description: Receives as input an object containing the intents from the + API Consumer and provides back the energy consumption with a callback. + operationId: calculateEnergyConsumption + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'energy-footprint-notification:calculate-energy-consumption' + requestBody: + description: Defines the application that provides the service and the + time period under analysis. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + responses: + "201": + description: The request has been acquired. The request identifier is + returned. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created resource + schema: + type: string + description: Link to the created resource + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + callbacks: + onEnergyConsumption: + $ref: "#/components/callbacks/onEnergyConsumptionCalculation" + /calculate-carbon-footprint: + post: + tags: + - Carbon footprint information retrieval + summary: Retrieves the overall carbon footprint for the target Application + instances in a certain period of time. + description: Receives as input an object containing the intents from the + API Consumer and provides back the carbon footprint with a callback. + operationId: calculateCarbonFootprint + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'energy-footprint-notification:calculate-carbon-footprint' + requestBody: + description: Defines the application that provides the service and the + time period under analysis. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + responses: + '201': + description: The request has been acquired. The request identifier is + returned. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created resource + schema: + type: string + description: Link to the created resource + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + callbacks: + onCarbonFootprintCalculation: + $ref: "#/components/callbacks/onCarbonFootprintCalculation" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onEnergyConsumptionCalculation: + # when data is sent, it will be sent to the callback url provided + "{$request.body.subscriptionRequest.sink}": + post: + summary: Provides back the result of the analysis on the energy + consumption + description: once the system has calculated the energy consumption of + the service, this information is provided back to the API Consumer + operationId: energyConsumptionNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the calculated energy consumption + required: true + content: + application/cloudevents+json: + schema: + allOf: + - $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.energy-footprint-notification.v1.energy" + specversion: "1.0" + datacontenttype: "application/json" + data: + requestId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + energyConsumption: 12.87 + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + onCarbonFootprintCalculation: + # when data is sent, it will be sent to the callback url provided + '{$request.body.subscriptionRequest.sink}': + post: + summary: Provides back the result of the analysis on the carbon + footprint + description: once the system has calculated the carbon footprint of + the service, this information is provided back to the API Consumer + operationId: carbonFootprintNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the calculated energy consumption + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.energy-footprint-notification.v1.carbon-footprint" + specversion: "1.0" + datacontenttype: "application/json" + data: + requestId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + carbonFootprint: 45.568 + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + ############################################################################ + # Resources # + ############################################################################ + schemas: + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 2 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.energy-footprint-notification.v1.energy + - org.camaraproject.energy-footprint-notification.v1.carbon-footprint + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.energy-footprint-notification.v1.energy + - org.camaraproject.energy-footprint-notification.v1.carbon-footprint + ReportCreationRequest: + description: resource containing the service under analysis and the + callback information for the API Consumer to be notified with the + results of the analysis. If no "timePeriod" is provided the analysis + is performed from the activation of the first instance of the + Application. + type: object + properties: + service: + type: array + description: list of Application Instance Identifiers. This are the + instances of the applications producing the service under analysis. + items: + $ref: '#/components/schemas/AppInstanceId' + timePeriod: + $ref: "#/components/schemas/TimePeriod" + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + requestId: + type: string + description: Identifier for the request. This + parameter is returned by the API and must be used to update it. + readOnly: true + required: + - service + - subscriptionRequest + AppInstanceId: + type: string + format: uuid + description: | + A globally unique identifier associated with a running + instance of an application. + Edge Cloud Platform generates this identifier when the + instantiation in the Edge Cloud Zone is successful + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required in + CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + required: + - startDate + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.energy-footprint-notification.v1.energy: "#/components/schemas/CloudEventEnergy" + org.camaraproject.energy-footprint-notification.v1.energy.error: "#/components/schemas/CloudEventError" + org.camaraproject.energy-footprint-notification.v1.carbon-footprint: "#/components/schemas/CloudEventCarbonFootprint" + org.camaraproject.energy-footprint-notification.v1.carbon-footprint.error: "#/components/schemas/CloudEventError" + CloudEventEnergy: + description: provides back the energy consumption for the service. The + result of the analysis is a floating point number. The unit of measure + is Kw/h. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + type: object + description: Event details payload + properties: + requestId: + type: string + description: Identifier for the request. This + parameter correlates this response with the request. + readOnly: false + energyConsumption: + type: number + format: float + example: 12.345 + description: the energy consumption for all the instances of the + service. The API is asynchronous, for this reason the value will be + returned back via a callback + CloudEventCarbonFootprint: + description: provides back the carbon footprint of the service. The result + of the analysis is a floating point number. The unit of measure is + tonnes. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + type: object + description: Event details payload + properties: + requestId: + type: string + description: Identifier for the request. This + parameter correlates this response with the request. + readOnly: false + carbonFootprint: + type: number + format: float + example: 45.568 + description: the carbon footprint for all the instances of the + service. The API is asynchronous, for this reason the value will be + returned back via a callback + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Responses # + ############################################################################ + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. Access token does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ENERGY_FOOTPRINT_NOTIFICATION.UNKNOWN_APPLICATION_IDENTIFIER + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Application Identifier unknown + value: + status: 404 + code: ENERGY_FOOTPRINT_NOTIFICATION.UNKNOWN_APPLICATION_IDENTIFIER + message: The target application is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - ENERGY_FOOTPRINT_NOTIFICATION.TIME_PERIOD_OUT_OF_RANGE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_TIME_PERIOD_OUT_OF_RANGE: + description: The parameter "timePeriod" in the request doesn't provide a correct range. The range can be too long with respect to the maximum possibile duration supported by the platform. Or startDate/endDate are not choerent with the API subscription. + value: + status: 422 + code: ENERGY_FOOTPRINT_NOTIFICATION.TIME_PERIOD_OUT_OF_RANGE + message: The requested time period for the evaluation is not a valid range. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1/raw.md b/marked/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..da26795cb62cb85948ab9b58eb4a5ee2d1ddcf38 --- /dev/null +++ b/marked/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1/raw.md @@ -0,0 +1,13 @@ + + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service Provider has a partnership with the Telco Operator and instantiates applications in different Edge Data Centers of the Telco Operator. These application instances, altogether, provide a Service offered to End Users that are also subscribers of the Telco Operator. The Service, with this configuration, offers better network performances to the End Users. Service Provider wants to know the E2E energy consumption and CO2 emission of its Service in a certain period of time. A system of the Service Provider invokes the Energy Footprint Notification API to get the above-mentioned information. The reported energy consumption and CO2 emissions consider the energy used to run the instances of those applications in the Data Centers and the energy consumption along the network to provide the Service (e.g., RAN and Core Network consumption) in the specified period of time.| M | +|Roles, Actor(s) and scope|• Service Provider: role of EFN API consumer
                      API Provider: role of EFN API provider
                      • Operator Platform ([EdgeCloud/documentation/SupportingDocuments/Edge terminology/edge_terminology.md at main · camaraproject/EdgeCloud](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/Edge%20terminology/edge_terminology.md)): role of Service host
                      • End User: both Teclo Operator's subscribers and Service Provider customer, role of Service consumer
                      • Scope: Computing Services (OGW Taxonomy)| M | +|NF Requirements|NA| O | +|Pre-conditions|• The Service Provider onboarded applications on the Operator Platform
                      • The Service Provider requested the deployment of some instances of those applications
                      • The Service Provider identifies the Services as collection of application instances
                      • The Service provided by those instances is up and running.
                      • The End Users are consuming the Service| M | +|Begins when|The API Consumer invokes the EFN API to get the Energy consumption of the Service, composed by a set of application instances, in a specific time period.| M | +|Step 2|The API Provider returns the overall Energy consumption of the Service in that specific time period.| M| +|Step 4|The API Consumer invokes the EFN API to get the Carbon footprint of the Service, composed by a set of application instances, in a specific time period.| M | +|Step 5|The API Provider returns the Carbon footprint of the Service in that specific time period.| M| +|Post-conditions|The Service Provider is aware of the Energy consumption and of the Carbon footprint of the Service in the selected time periods| M | diff --git a/marked/EnergyFootprintNotification/documentation/API_documentation/README/raw.md b/marked/EnergyFootprintNotification/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/EnergyFootprintNotification/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist/raw.md b/marked/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..814f209ddfc96a434632744bdb766bdeae7aed87 --- /dev/null +++ b/marked/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist/raw.md @@ -0,0 +1,28 @@ + + +# API Readiness Checklist + +Checklist for API energy-footprint-notification 0.1.0 in r1.3 + + + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/energy_footprint_notification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | 0.1.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/EFN_UserStory_UseCase_1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [Test-EC](/code/Test_definitions/energy-footprint-notification-calculateEnergyConsumption.feature), [Test-CF](/code/Test_definitions/energy-footprint-notification-calculateCarbonFootprint.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101707/EnergyFootprintNotification+API+description) | + + + + + diff --git a/marked/EnergyFootprintNotification/documentation/SupportingDocuments/README/raw.md b/marked/EnergyFootprintNotification/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/EnergyFootprintNotification/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/HighThroughputElasticNetworks/README/raw.md b/marked/HighThroughputElasticNetworks/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b1ca34275458294f54ddd15f3b1f3b57e5834e1f --- /dev/null +++ b/marked/HighThroughputElasticNetworks/README/raw.md @@ -0,0 +1,39 @@ + + + + + + + + + +# HighThroughputElasticNetworks + +Sandbox API Repository to describe, develop, document, and test the HighThroughputElasticNetworks Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/wQAkAw) + +## Scope + +* Service APIs for “HighThroughputElasticNetworks” (see APIBacklog.md) +* The API provides the customer with the ability to: + * This API provides scheduling ability of huge data transmission in network. It can calculate load-balancing paths automatically with given time duration, total data amount and bandwidth limit, and satisfy huge data transmission requirements with dynamic and elastic bandwidth allocation algorithms, tidal-traffic-aware segment list adjustment and SRv6 multiple segment list technology.
                      This API is designed for large enterprises requiring efficient network bandwidth management. It dynamically adjusts and optimizes bandwidth utilization to handle high-volume data transmission scenarios such as video conferences, large file transfers, and cloud resource access. By leveraging advanced technologies, it ensures seamless and efficient data flow across different time periods. This API is ideal for organizations that need robust solutions to manage substantial data transfers, ensuring high performance and reliability in demanding network environments.
                      This API is suitable for customers in industries with massive data transfer requirements, such as Cross-cloud backup, model training at intelligent compute centers, video editing, and scientific computing. For example, the Five-hundred-meter Aperture Spherical radio Telescope (FAST), located in GuiZhou province of China, could generate more than 10 PB of observational data per year. By calling this API, users can dynamically adjust bandwidth and elastically orchestrate network resources according to their specific requirements for bandwidth, latency, and file size. This capability facilitates the efficient and expedient transmission of large observational datasets within short timeframes. In subsequent applications of the API, developers can set multiple groups of input parameters as standard configuration files, enabling quick selection and application.

                      Input:
                      1. Bandwidth Requirement: Time-segmented bandwidth requirements (can include multiple time points)
                      2. Bandwidth Requirement Type: Upload bandwidth, download bandwidth, two-way bandwidth Service
                      3. Latency Requirement: Latency guarantee requirement range
                      4. File Requirements: Size of files to be transmitted
                      5. Guarantee Requirements: Bandwidth guarantee and load sharing requirements

                      Output:
                      1. Success or failure
                      2. Estimation of transmission rate by time segment
                      3. Estimated transmission duration,
                      4. Statistical conclusions after successful transmission1. Estimation of transmission rate by time segment
                      5. (optional) any conditions required for the operator to meet the request (e.g. a particular entry point to the network must be used). +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: !! tbd + * [Registration / Join](https://wiki.camaraproject.org/x/TQAG) !! Update this link with your meeting registration/join link + * Minutes: Access [meeting minutes] !! update this link to your wiki page using the "Share" link +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/HighThroughputElasticNetworks/code/API_definitions/README/raw.md b/marked/HighThroughputElasticNetworks/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/HighThroughputElasticNetworks/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/HighThroughputElasticNetworks/documentation/API_documentation/README/raw.md b/marked/HighThroughputElasticNetworks/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/HighThroughputElasticNetworks/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/HighThroughputElasticNetworks/documentation/SupportingDocuments/README/raw.md b/marked/HighThroughputElasticNetworks/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/HighThroughputElasticNetworks/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/HomeDevicesQoD/README/raw.md b/marked/HomeDevicesQoD/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..392857e260a61cd29f5d41e3a429dbfeab8af980 --- /dev/null +++ b/marked/HomeDevicesQoD/README/raw.md @@ -0,0 +1,62 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#283](https://github.com/camaraproject/APIBacklog/issues/283) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase D – Repository With Reviewed Release](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# HomeDevicesQoD + +Sandbox API Repository to describe, develop, document, and test the HomeDeviceQoD Service API. The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/4TLe) + +## Scope +* Service APIs for “HomeDevicesQoD” (see APIBacklog.md) +* It provides the customer with the ability to: + * change, on demand, the desired QoS behaviour for the IP traffic corresponding to a specific user home device. +* Describe, develop, document and test the APIs +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/r1.2) (Fall24), with the following API versions: + * **home-devices-qod v0.4.0** + [[YAML]](https://github.com/camaraproject/HomeDevicesQoD/blob/r1.2/code/API_definitions/home-devices-qod.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/r1.2/code/API_definitions/home-devices-qod.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/r1.2/code/API_definitions/home-devices-qod.yaml) +* The latest public release is always available here: https://github.com/camaraproject/HomeDevicesQoD/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/HomeDevicesQoD/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/HomeDevicesQoD/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://teams.microsoft.com/l/meetup-join/19%3ameeting_NzJkZDc4MjktNjU1YS00NzYxLWExNzgtZDlmNzI5MmMxMGNi%40thread.v2/0?context=%7b%22Tid%22%3a%229744600e-3e04-492e-baa1-25ec245c6f10%22%2c%22Oid%22%3a%22458d45b0-4ca7-41e2-a7b3-3d722abf4468%22%7d) (Microsoft Teams Meeting) + * Schedule: ~~bi-weekly~~ on demand(*), Thursday, 4:30pm CET. + * **(*)NOTE: The project is currently stable, so meetings will be scheduled according to the needs of the working group participants. Offline updates will be provided on the mailing list as needed instead.** If anyone in the working group would like to have one of the following meetings, please send an email to the list and/or open a new issue in the repository so that everyone can keep track of new topics to discuss. + * Minutes: Access [meeting minutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . + diff --git a/marked/HomeDevicesQoD/code/API_definitions/home-devices-qod/raw.md b/marked/HomeDevicesQoD/code/API_definitions/home-devices-qod/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2de704be3bbf9df2d8951c3fb0a382c086628fb3 --- /dev/null +++ b/marked/HomeDevicesQoD/code/API_definitions/home-devices-qod/raw.md @@ -0,0 +1,366 @@ +# home-devices-qod + +```yaml +openapi: 3.0.3 +info: + title: Home Devices QoD + description: | + Service Enabling Network Function API for *QoS-on-demand* (QoD) control applied to devices connected to the user's home network. API clients can request to change, on demand, the desired QoS behaviour for the IP traffic corresponding to a specific user home device. The QoS behaviour is determined by the Service Class provided by the API Client, which is mapped to a DSCP value according to [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines. + + # Introduction + + It may be useful for application developers to request on-demand QoS behaviours (service classes) to be configured at the user's home WiFi access point to ensure the required quality of experience for those services/applications running on a specific home device. + + For example, the QoD control capability could be useful in scenarios such as: + + - A user using head-mounted display device for VR/AR applications. VR/AR applications require high bandwidth for the big amount of data to be streamed. + - A user using VoIP application in a home device. Lower latency improves call quality or avoids dropped calls. + + Generally speaking, QoS on demand may improve the qualty of experience for real time services like Videocomms, Cloud Gaming and Virtual Reality. + + ![Videocomms DSCP usage example](https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/main/documentation/API_documentation/resources/videocomm_dscp_example.png) + + # Relevant terms and definitions + + - **Home Device**: + User device connected to the user's home network. + + - **Service Class**: + A statement of the required QoS characteristics of a traffic aggregate. Conceptually, a service class refers to applications with similar characteristics and performance requirements. + + - **DSCP**: + *Differentiated Services (DiffServ) Code Point*. DiffServ is a simple and scalable mechanism for classifying and managing network traffic and providing quality of service (QoS) on IP networks. The DSCP value will be used to classify the traffic of the target home device in order to be treated accordingly. + + # API Functionality + + This API allows to third party clients to set, on demand, the desired QoS behaviour (service class) associated to the traffic of the device connected to the user's home network that matches the input criteria provided. The device traffic is classified (by DSCP) and treated accordingly. + + - **NOTE: The scope of the API is as follows**: + - QoS treatment is applied to a target user device **only within the user's home network** (i.e., between the device and the home router) + - QoS treatment **only applies to downstream IP traffic** (i.e., from the home router to the target device) + - QoS treatment **only applies to home devices using WiFi access** (i.e., home router WiFi interface) + + The API provides a single endpoint/operation: + + - Set the desired QoS behaviour for a user home device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details on how a client requests an access token. Please refer to Identify and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the Profile. + + Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + In the case of the Home Devices QoD API scenario and according to the API definition, 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This can be done via IP-based authentication (i.e. using the public IP of the device in this case). + + The 3-legged access of the Home Devices QoD API could also be combined with end-user consent management, depending on the legal basis applied. User consent would be required before personal data is processed by API clients for a specific purpose. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.4.0 + x-camara-commonalities: 0.4.0 +servers: + - url: "{apiRoot}/home-devices-qod/v0.4" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /qos: + put: + summary: Set the desired QoS behaviour for a user home device + description: | + Set the desired QoS behaviour for the traffic corresponding to the user home device matching the input criteria. **QoS behaviour is determined by the service class provided by the API Client. Setting `standard` service class restores default traffic treatment for the target home device.** + + - The operation is executed for the user whose `sub` is in the access token used to call this endpoint, and for the home network also deducted from the information included in the access token. + - The target user device is identified by the internal IP address of that device in the home network. + - In case there is no device matching the input criteria, the operation returns a 404 error. + tags: + - Home Devices QoD + operationId: setQos + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/QosOnDemandUpdate" + example: + serviceClass: real_time_interactive + ipAddress: 192.168.1.27 + required: true + responses: + "204": + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + description: Requested QoS passed all validations and was applied + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/setQosPermissionDenied403" + "404": + $ref: "#/components/responses/setQosNotFound404" + "409": + $ref: "#/components/responses/setQosConflict409" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/setQosServiceUnavailable503" + "504": + $ref: "#/components/responses/Generic504" +components: + schemas: + QosOnDemandUpdate: + type: object + description: Payload to change the QoS behaviour associated to a home device. + required: + - serviceClass + - ipAddress + properties: + serviceClass: + type: string + description: | + The name of the service class requested by the API client. It is associated with QoS behaviours optimised for a particular application type. Each service class is mapped to a DSCP value according to [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines. The DSCP value is used to classify the target home device's traffic so that it can be treated accordingly (i.e. to meet its QoS needs). + + The following service classes are supported: + + | Service Class Name | DSCP Name | DSCP value (decimal) | DCSP value (binary) | Application Examples | + |-----------------------|-----------|----------------------|---------------------|-----------------------------------------------| + | Real-Time Interactive | CS4 | 32 | 100000 | Video conferencing and Interactive gaming | + | Multimedia Streaming | AF31 | 26 | 011010 | Streaming video and audio on demand | + | Broadcast Video | CS3 | 24 | 011000 | Broadcast TV & live events | + | Low-Latency Data | AF21 | 18 | 010010 | Client/server transactions Web-based ordering | + | High-Throughput Data | AF11 | 10 | 001010 | Store and forward applications | + | Low-Priority Data | CS1 | 8 | 001000 | Any flow that has no BW assurance | + | Standard | DF(CS0) | 0 | 000000 | Undifferentiated applications | + enum: + - real_time_interactive + - multimedia_streaming + - broadcast_video + - low_latency_data + - high_throughput_data + - low_priority_data + - standard + example: real_time_interactive + ipAddress: + type: string + format: ipv4 + description: Internal IP address of the connected device in the LAN. + example: 192.168.1.27 + ErrorInfo: + type: object + required: + - message + - status + - code + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials + setQosPermissionDenied403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: User home network cannot be deducted from access token context + setQosNotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + NotFound: + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found + NoDeviceMatch: + value: + status: 404 + code: DEVICE_NOT_FOUND + message: No connected device found for the input criteria provided + setQosConflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Conflict: + value: + status: 409 + code: CONFLICT + message: Conflict with the current state of the target resource + TooManyDevices: + value: + status: 409 + code: HOME_DEVICES_QOD.TOO_MANY_DEVICES + message: Exceeded the maximum quantity of devices with non-default QoS behaviour + RssiBelowThreshold: + value: + status: 409 + code: HOME_DEVICES_QOD.RSSI_BELOW_THRESHOLD + message: RSSI from device is below allowed threshold + QosTooHigh: + value: + status: 409 + code: HOME_DEVICES_QOD.QOS_TOO_HIGH + message: Requested QoS is higher than the maximum QoS allowed + OccupancyAboveThreshold: + value: + status: 409 + code: HOME_DEVICES_QOD.OCCUPANCY_ABOVE_THRESHOLD + message: The occupancy is above the allowed threshold + NotConnectedToRequiredInterface: + value: + status: 409 + code: HOME_DEVICES_QOD.NOT_CONNECTED_TO_REQUIRED_INTERFACE + message: Device is not connected to the required interface (e.g. WiFi 5GHz interface) + NotSupportedRequiredInterface: + value: + status: 409 + code: HOME_DEVICES_QOD.NOT_SUPPORTED_REQUIRED_INTERFACE + message: Device does not support required interface (e.g. WiFi 5GHz interface) + QosAlreadySetToDefault: + value: + status: 409 + code: HOME_DEVICES_QOD.QOS_ALREADY_SET_TO_DEFAULT + message: Device QoS is already set to default value + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: Server error + setQosServiceUnavailable503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Unavailable: + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable + RouterOffline: + value: + status: 503 + code: HOME_DEVICES_QOD.ROUTER_OFFLINE + message: Router is not online. Try it later + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: Request timeout exceeded + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + securitySchemes: + openId: + description: | + OpenID Connect 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This can be done via IP-based authentication (i.e. using the public IP of the device in this case). + + The 3-legged access of the Home Devices QoD API could also be combined with end-user consent management, depending on the legal basis applied. User consent would be required before personal data is processed by API clients for a specific purpose. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration +security: + - openId: + - home-devices-qod:qos:write +tags: + - name: Home Devices QoD + description: QoD control operations for home devices +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/HomeDevicesQoD +``` diff --git a/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist/raw.md b/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..52edc058711f72f329bffff1637d46f089c0df0f --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist/raw.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for home-devices-qod 0.4.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Comments | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [home-devices-qod.yaml](/code/API_definitions/home-devices-qod.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded in [API definition](/code/API_definitions/home-devices-qod.yaml) | +| 6 | User stories | O | O | O | M | Y | [home-devices-qod-User-Stories.md](/documentation/API_documentation/home-devices-qod-User-Stories.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [home-devices-qod.feature](/code/Test_definitions/home-devices-qod.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [home-devices-qod.feature](/code/Test_definitions/home-devices-qod.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/xxx) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Comments column, provide the link to the asset once available, and any other relevant comments. + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: [API Readiness Checklist](https://wiki.camaraproject.org/x/HQBFAQ) diff --git a/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories/raw.md b/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..85f3cd88b13f601ebcde68c6499278008297f060 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories/raw.md @@ -0,0 +1,11 @@ +**User Story: Configure traffic profile (DSCP)** +
                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) specific QoS behaviours (service classes) to be configured at my end-user's home WiFi access point to ensure the required quality of experience I need for my service/app. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                      **Actors:** Application service providers, hyperscalers, application developers.
                      **Scope:** Configure QoS behaviours to ensure needed quality of experience for a given device within a residential LAN. The expected behaviour is that the target device is the same device where the app is running. | +| ***Pre-conditions*** |The preconditions are listed below:
                      1. The end-user is connected to a residential WiFi access point.
                      2. The end-user is running an application/service developed by the customer (application developer) that includes calls to the API.
                      3. Security and privacy requirements are fulfilled as defined in Commonalities.
                      | +| ***Activities/Steps*** | **Starts when:** The server/backend service calls the API specifying the service class required and the target device.
                      **Ends when:** The requested QoS behaviour (service class) has been configured and the server/backend has being informed about it.
                      | +| ***Post-conditions*** | Service class is applied and customer (application developer) app/service continues.
                      Note that default QoS behaviour could be restored on back-end side at a given frequency (e.g. daily) or on demand by customer doing another call to the API.| +| ***Exceptions*** | Several exceptions might occur during the Home Devices QoD API operations
                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                      • Invalid input: Not valid input data to invoke operation (e.g. invalid IP address, invalid service class, etc).
                      • Denied by carrier: QoS behaviour cannot be implemented (already too many QoS behaviours configured, device is not connected to the required interface, etc), Server error, Service unavailable, request time exceeded, etc.
                      | diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3b18aa44c5d2a7ac2bc28325a395725b019581b1 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17/raw.md @@ -0,0 +1,41 @@ +# Camara Home Devices QoD meeting + +*17/11/2022* + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Anne Matthieu (Orange) +* Flury Thibaud (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes: [https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Kick-off follow-up meetings +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Kick-off** | | +| | Telefonica provides a general view of the API value proposition and a general review of the API YAML definition already uploaded to the github repository. Waiting feedback from partners | +| **Recap & Recent Updates** | | +| |
                      • Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                      • Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues) 
                      • Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls)
                      | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                    7. [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| **New Issues** | | +| | none | +| **AOB** | | +| | Next Home Devices QoD community call on Nov 24th, UTC 16:00, CET 17:00 | diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e193141bc4dc4b5fec341b0da7b5328af128f046 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24/raw.md @@ -0,0 +1,48 @@ +# Camara Home Devices QoD meeting + +## Meeting Information +**Meeting Date:** 24/11/2022 + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Sylvain Morel (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes link: +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                      +Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                      +Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +## Discussion Items + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                      • DT will be joining to github repository and will be participating soon in the API definition. Waiting contact person/s from DT to invite them to participate.
                      • Orange request to provide some further information about the user stories being considered by TEF. And they propose to upload the user stories information following the corresponding template as done for [Carrier Billing API](https://github.com/alabajnaid/CarrierBillingCheckOut/blob/api_user_stories/documentation/API_documentation/carrier_billing_user_stories.md). They will use it for internal marketing purposes having a better understanding of what it is being proposed for Home Devices QoD API.
                      • TEF request some feedback from Orange regarding the technical feasibility of the API from their side and/or some feedback on the API definition itself. | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| **New Issues** | | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) Aligment with API Design Guidelines Commonality. Being addressed in PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)
                      • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md) | +| **AOB** | | +| | Next Home Devices QoD community call on Dic 1st, UTC 16:00, CET 17:00 | + +## Next Steps + +* TEF will upload a 1st draft of user stories document in https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/API_documentation +* Orange to provide feedback on user stories and API definition. \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8ece95e72b732116039c744ccd7c02e2debfae57 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01/raw.md @@ -0,0 +1,48 @@ +# Camara Home Devices QoD meeting + +## Meeting Information +**Meeting Date:** 01/12/2022 + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Sylvain Morel (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes link: +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                        +Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                        +Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +## Discussion Items + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                        • Still waiting technical contacts from DT to get them involved in github project and API design. PING done to DT this week. They are working on it
                        • No further updates... | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                          The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                        • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) Aligment with API Design Guidelines Commonality. Being addressed in PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)
                        • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md) | +| **New Issues** | | +| | [#9](https://github.com/camaraproject/HomeDevicesQoD/issues/9) Upload first version of user stories doc in API documentation. Being addressed in PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10).

                          Comments received from Orange (Robert Ludovic) already answered in the PR itself. It has been agreed to include [some additional clarifications](https://github.com/camaraproject/HomeDevicesQoD/pull/10#issuecomment-1333796244) in the user story doc before merge it. | +| **AOB** | | +| | Next Home Devices QoD community call on Dic 15th, UTC 16:00, CET 17:00 (Dic 8th is bank holiday in Spain) | + +## Next Steps + +* TEF to update PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10) with agreed changes. diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ffcb7d1d346a2048e85c12249703d104595f5bd7 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12/raw.md @@ -0,0 +1,56 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 12/01/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Robert Ludovic (Orange) +* Rafal Artych (DT) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                          +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                          +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                          +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                        • MERGED PR [12](https://github.com/camaraproject/HomeDevicesQoD/pull/12) Fix version number typo in api definition -> Fix version number typo in api definition YAML file as it should be v0.1.0 (representing the first API proposal) and not yet v1.0.0.

                        • API version v0.1.0 is merged in `main` branch including API definition YAML file, user stories doc file (PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10)) and API documentation file (PR [#15](https://github.com/camaraproject/HomeDevicesQoD/pull/15)). This API version corresponds to the one TEF will bring to MWC.

                        • A new branch `dev-v0.2.0` has been created including some minor changes: 1) "*Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*" (PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) replacing PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)) and 2) "*403 specific API error when User home network cannot be deducted from access token*" (PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14)). Furhter changes in API definition (if any) will be addressed in this version or subsequent versions.

                        • Working with Noel Wirzius to get technical contact/s from DT and to get them involved in github project and API design. He was expected to provide information in the coming days but Rafal Artych (representing DT) has joined the call Today. He already have access to github repository and is subscribed to the mailing list. | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101).
                          API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                          To be CLOSED as soon DT contact/s are 100% confirmed.
                          • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                          | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) ~~Aligment with API Design Guidelines Commonality.~~
                          CLOSED. Addressed in PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) already MERGED (which replaced PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)).
                          • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md)
                          | +| | [#9](https://github.com/camaraproject/HomeDevicesQoD/issues/9) ~~Upload first version of user stories doc in API documentation~~
                          CLOSED. Addressed in PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10) already MERGED. | +| **New Issues** | | +| | [#16](https://github.com/camaraproject/HomeDevicesQoD/issues/16) ~~Upload first version of API documentation~~
                          CLOSED. Addressed in PR [#15](https://github.com/camaraproject/HomeDevicesQoD/pull/15) already MERGED. | +| **AOB** | | +| |
                        • Next Home Devices QoD community call on Jan 19th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Get feedback from other CAMARA partners including Orange and DT after their internal promotion of the API. + * Robert Ludovic confirms that the API is not prioritized in Orange side for the short-term. Orange feedback on API and uses cases should be expected for the mid-term. + * Waiting DT potential feedback as soon as they manage the review the API information already uploaded to github. +* Move forward with CAMARA API milestones. + +
                          + +> Mailinglist:
                          Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                          The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1a81cda48c66502dbd639c41f70a905ad9a90c96 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19/raw.md @@ -0,0 +1,52 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 19/01/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                          +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                          +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                          +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                        • API doc updates for API version 0.2.0 being included in branch `dev-v0.2.0` (new issue [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18)). | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) ~~Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101).~~
                          CLOSED. The corresponding CAMARA Commonalities track has been closed with some agreements but not a unique traversal solution. Each API we work on will need to consider additional requirements (if any) to decide which identifiers makes the most sense. So far, in case of Home Devices QoD current definition, it's assumed user authentication (3-legged token). And the user and home network information are deducted from the information included in the access token. There is no user identifier filed included in the API request body. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                          To be CLOSED as soon DT contact/s are 100% confirmed.
                          • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                          Working with Noel Wirzius to get technical contact/s from DT and to get them involved in github project and API design. He was expected to provide information during this days. Still no confirmation received from him. So far Rafal Artych (representing DT) is joining weekly calls. He has confirmed that he is speaking with Noel already and next week they hope to be able to confirm who the contact person/s will be. | +| **New Issues** | | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                          Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                          • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                          • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                          | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                          It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).
                        | +| **AOB** | | +| |
                      • Next Home Devices QoD community call on Jan 26th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Get the feedback DT may have about uses cases and API design. + * It will have to wait most likely until DT technical contact is confirmed. + +
                        + +> Mailinglist:
                        Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f694a41e561d543286220037246b4b4dd83dcdfb --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02/raw.md @@ -0,0 +1,51 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 02/02/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) +* Vaishali Gupta (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                        +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                        +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                        +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                      • Current project status will be reported to see the best way forward to meet the CAMARA API milestones.
                      • The call frequency will be re-evaluated to see if every two weeks is better for now.
                      • Our colleagues from DELL are joining the call for the first time. They belong to DELL engineering team and they are doing a preliminary overall evaluation of the CAMARA project and the more interesting API projects for them (like Home Devices QoD API in this case). According to Mike, for the moment they are not in position to provide feedback on the API design or API use cases.
                      • Rafal can't confirm when DT will provide feeback on the API design or use cases. DT`s technical department is currently discussing this issue and will come back. In today's call Rafal brings some personal suggestions for the API definition. It is agreed to create a Github issue for each of them to track the discussion and link them to the required PR if it is eventually needed. | +| **Open Issues** | | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                        To be CLOSED as soon DT contact/s are 100% confirmed.
                        • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                        Rafal can't confirm when the DT contact person(s) will be defined. He suggests to bring it up in the next SteerCo (next week). For the moment he will join the calls and keep the lights on. | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                        Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                        • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                        • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                        No further changes included last two weeks. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                        It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                        No updates on this one. Still not clear how it is going to be handled in CAMARA Commonalities.
                      | +| **New Issues** | | +| | N/A | +| **AOB** | | +| |
                    8. Next Home Devices QoD community call on Feb 9th, UTC 16:00, CET 17:00
                        (*)_To be confirmed depending on the call frequency re-evaluation_
                      | + + +## Next Steps + +* Get the feedback DT may have about uses cases and API design.
                      (*)_It will most likely have to wait until DT technical contact(s) are confirmed._ + +
                      + +> Mailinglist:
                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7616b6546e3fb87e56341cea4c8dfc6967816452 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15/raw.md @@ -0,0 +1,53 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 15/02/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                    9. The current status of the project was reported to SteerCo last week (including the matter of the DT technical contacts).
                    10. The call frequency will be set to every two weeks (same time slot). This is more appropriate for the time being, until DT’s engagement in the API discussions.
                    11. In the previous call Rafal brought some personal suggestions for the API definition. As agreed, a new Github issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) has been created to track the discussion and link it to the required PR if it is eventually needed. | +| **Open Issues** | | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                      To be CLOSED as soon DT contact/s are 100% confirmed.
                      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                      Rafal has no news in the matter of DT's technical contacts. No news is expected until after the Mobile World Congress. | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                      Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                      • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                      • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                      No further changes included in last two weeks. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                      No updates on this one. Still not clear how it is going to be handled in CAMARA Commonalities.
      | +| **New Issues** | | +| | [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) Reduction of network-specific terminolgy/acronyms
      This issue is actually aligned with Commonalities issue [#108](https://github.com/camaraproject/WorkingGroups/issues/108) and PR [#120](https://github.com/camaraproject/WorkingGroups/pull/120). From TEF side it is being validated inernally with the technical and business teams and a solution aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) is being considered. | +| **AOB** | | +| |
    6. Next Home Devices QoD community call on Mar 2nd, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Telefonica to provide a proposal to address issue #23. +* Get the feedback DT may have about uses cases and API design.
      (*) _It will have to wait until DT technical contact(s) are confirmed. Not before MWC._ + +
      + +> Mailinglist:
      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b96dcbc1a7053cfe770e28ed335dcce005891ac6 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16/raw.md @@ -0,0 +1,54 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 16/03/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
    7. Project adaptation to release/versioning guidelines agreed in Commonalities is done (issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27)).
    8. "Service class" included in [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) as relevant API term to update commonalities glossary with HomeDevicesQoD-subproject relevant terms.
    9. New API definition aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) has been included in release v0.2.0 (it resolves issue[#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23)).
    10. Update API documentation according to release 0.2.0 API version stopped until a final agreement is reached in Commonalities issue [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164)| +| **Open Issues** | | +| | ~~[#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers~~~.
      CLOSED. Rafal has been added as a maintainer (PR [#26](https://github.com/camaraproject/HomeDevicesQoD/pull/26).), as he is the contact person from DT who is actively involved in the project. And this issue has been closed, as there's no point in discussing it any further.
      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
      | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
      ~~Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19)~~.
      PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19) has been MERGED to `dev-v0.2.0` branch with current documentation status (i.e. NOT including Doc changes related to issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) and PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25)).
      This is part of the process described in issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) to adapt the project to the release/versioning policy agreed in Commonalities, i.e. the `main` branch is assumed to be the latest. Documentation work corresponding to API release v0.2.0 (when resumed) will be done against the `main' branch until release v0.2.0 is agreed to be closed.

      On the other hand, there is a new issue in the Commonalities project [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164) that affects this. Basically because the way the CAMARA APIs are documented is being rethought. It is proposed not to have separate documentation at all, but to embed all documentation in the OAS definition itself (YAML). The Home Devices QoD spec file is already quite self-documented, so I'll wait for the final agreement in Commonalities to complete the documentation for release 0.2.0 to avoid unnecessary overhead. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

      Added "Service Class" as a representative term for this API.| +| | ~~[#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) Reduction of network-specific terminolgy/acronyms~~
      This issue is actually aligned with Commonalities issue [#108](https://github.com/camaraproject/WorkingGroups/issues/108) and PR [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

      CLOSED. On the TEF side, after internal validation with the technical and business teams, a new API definition aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) was provided in PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25). The changes made were approved by Rafal (DT) and Robert Ludovic (Orange) and the PR was MERGED. | +| **New Issues** | | +| | ~~[#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) Adapt project to release/versioning guidelines agreed in Commonalities~~
      Commonalities track: https://github.com/camaraproject/WorkingGroups/pull/123.

      CLOSED already. Steps accomplished:
      • ~~PR to merge v0.1.0 changelog into the main branch.~~ >> DONE. PRs [#28](https://github.com/camaraproject/HomeDevicesQoD/pull/28) (added CHANGELOG) and [#29](https://github.com/camaraproject/HomeDevicesQoD/pull/29) (typo fix)
      • ~~The merge commit from PR will be tagged as v0.1.0, and will get the v0.1.0 release branch.~~ >> DONE https://github.com/camaraproject/HomeDevicesQoD/releases
      • ~~Merge the dev-v0.2.0 branch into main, so that it contains the latest stable API definition state as agreed.~~ >> DONE. PR [#30](https://github.com/camaraproject/HomeDevicesQoD/pull/30)
      • ~~Update README.md accordingly..~~ >> DONE. PR [#31](https://github.com/camaraproject/HomeDevicesQoD/pull/31)
      | +| **AOB** | | +| |
    11. Next Home Devices QoD community call on Mar 30th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create a new PR to align API spec files with pending traversal Commonalities issues like: CamelCase usage (issue [#157](https://github.com/camaraproject/WorkingGroups/issues/157)), error schema definitions (issue [#151](https://github.com/camaraproject/WorkingGroups/issues/151)), API documentation (issue [#164](https://github.com/camaraproject/WorkingGroups/issues/164)), etc... +* When this is done, generate the first stable API release and continue with the CAMARA milestones to complete it, as no further functionality will be added for the time being. + +
      + +> Mailinglist:
      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5ff723418aa139d31c31db45a3f02c9e92781945 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30/raw.md @@ -0,0 +1,56 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 30/03/2023 + +### Attendees + +* Mona Mokhber (Telefonica) +* Diego Rivera Nuñez (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
    12. [#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33) created to align the API with the new guideline agreements| +| **Open Issues** | | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
      ~~Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19)~~.
      PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19) has been MERGED to `dev-v0.2.0` branch with current documentation status (i.e. NOT including Doc changes related to issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) and PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25)).
      This is part of the process described in issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) to adapt the project to the release/versioning policy agreed in Commonalities, i.e. the `main` branch is assumed to be the latest. Documentation work corresponding to API release v0.2.0 (when resumed) will be done against the `main' branch until release v0.2.0 is agreed to be closed.

      On the other hand, there is a new issue in the Commonalities project [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164) that affects this. Basically because the way the CAMARA APIs are documented is being rethought. It is proposed not to have separate documentation at all, but to embed all documentation in the OAS definition itself (YAML). The Home Devices QoD spec file is already quite self-documented, so I'll wait for the final agreement in Commonalities to complete the documentation for release 0.2.0 to avoid unnecessary overhead. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

      Added "Service Class" as a representative term for this API.| +| **New Issues** | | +| | [#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33) Align API spec format with the latest Commonalities agreements
      This issue is to align API spec format with the latest Commonalities agreements
    13. Commonalities - adjust the error `status` field, which will eventually be an integer (not a patterned string): PR [#145](https://github.com/camaraproject/WorkingGroups/pull/145).
    14. Commonalities - adjust the schema references in the errors responses and apply the agreed solution: Issue [#151](https://github.com/camaraproject/WorkingGroups/issues/151) & PR [#162](https://github.com/camaraproject/WorkingGroups/pull/162).
    15. Commonalities - change the format of the API fields to lowerCamelCase: Issue [#157](https://github.com/camaraproject/WorkingGroups/issues/157), Discussion [#169](https://github.com/camaraproject/WorkingGroups/discussions/169) & PR [#171](https://github.com/camaraproject/WorkingGroups/pull/171).
      The changes were approved by Ludovic (Orange) pending to be approved by Rafal (DT) in order to get merged. | +| **AOB** | | +| |
    16. Next Home Devices QoD community call on Apr 13th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* [PR#34](https://github.com/camaraproject/HomeDevicesQoD/pull/34) to get approved by pending reviewers and will be merged and closed afterwards (along with its related [issue#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33)) + +* The note from last meeting is still pending: +***"Generate the first stable API release and continue with the CAMARA milestones to complete it, as no further functionality will be added for the time being."*** + +* No furthur issues were discussed during the meeting. + +
      + +> Mailinglist:
      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a99eeaed99ee57fb7d40583a602773cb82570907 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08/raw.md @@ -0,0 +1,59 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 08/06/2023 + +### Attendees + +| Companies | Attendees | +| --------- | --------- | +| Telefónica | Jesús Peña, Eber Marins, Christian Duran | + +
      + +**No other WG participants joined today's call, so these meeting notes are provided as an offline update for the record**... + +
      + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +
      + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +
      + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
    17. Current project status: 2 open issues and no ongoing PRs.
    18. Issue 18 "v0.2.0 - Update API documentation according to v0.2.0 API version" has been CLOSED. Addressed in PR #30 which has been already merged.
    19. PR #40 "Creation of API readiness checklist document (Issue 39)" has been merged. It is related to open issue #39.
    20. New issue #41 "WiFi QoS Mappings" | +| **Open Issues** | | +| |
    21. ~~[#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) "v0.2.0 - Update API documentation according to v0.2.0 API version"~~
      CLOSED. This issue was addressed in PR ~~[#38]((https://github.com/camaraproject/HomeDevicesQoD/pull/38))~~ which has already been merged. The PR updates the API documentation according to v0.2.0 API version definition, including changes from v0.1.0 release, and adds the documentation to the API definition as discussed in issue [#64](https://github.com/camaraproject/WorkingGroups/issues/164) of Commonalities. This PR is in line with what it is being done in other subprojects (such as [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand/pull/151)).
      • This was the only remaining change before closing and creating the v0.2.0 release on github.
      | +| | [#39](https://github.com/camaraproject/HomeDevicesQoD/issues/39) "Generation of release v1.0.0"
      Issue to validate and meet API readiness requirements to generate a first stable API release v1.0.0 from v0.2.0. No further functionality will be added to the API. The requirements in order to generate a release v1.0.0 in CAMARA APIs are being discussed in Commonalities (Issue [#139](https://github.com/camaraproject/WorkingGroups/issues/139)). The corresponding release v1.0.0 would be generated in the github project.
      • ~~PR [#40](https://github.com/camaraproject/HomeDevicesQoD/issues/39) - "Creation of API readiness checklist document (Issue 39)"~~
        MERGED. The "home_devices_qod_readiness_checklist.md" document with the API readiness status [is now available](https://github.com/camaraproject/HomeDevicesQoD/blob/main/documentation/API_documentation/home_devices_qod_readiness_checklist.md) as done in the [QualityOnDemand project](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoD-API-Readiness-Checklist.md)
      • The requirement to fulfill step 5 ("API test cases and documentation") of the API Readiness checklist is being discussed in issue [#61](https://github.com/camaraproject/WorkingGroups/issues/61) of Commonalities. Need to confirm mandatory deliverable(s) and whether it is good enough to provide the ".feature" file or not.
      | +| **New Issues** | | +| | [#41](https://github.com/camaraproject/HomeDevicesQoD/issues/41) "WiFi QoS Mappings"
      Open by DT (Rafal), it is intended to refer to [RFC8325](https://datatracker.ietf.org/doc/html/rfc8325) in the documentation as the standard reference for WiFi downstream. From Telefonica's point of view, there is no need to do this as the current API design is not related to RFC8325 or IEEE 802.11 UP (User Priority). The current proposal is based on the DSCP value set in the user's home router to control the QoS behaviour of the target home device's IP traffic. And it has been defined the "service class" concept on top of DSCP to provide a developer-friendly design following RFC4594 recommendations. So existing documented service class mapping to DSCP should be sufficient. | +| **AOB** | | +| |
    22. Next Home Devices QoD community call on June 21st, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create issue and PR to generate v0.2.0 release on github. +* Continue discussion on issue #39 "Generation of release v1.0.0".
      • If providing a ".feature" file is confirmed as the minimum mandatory deliverable, then create PR to provide the ".feature" file as the API test cases definition.
      +* Close discussion on issue #41 "WiFi QoS Mappings". + +
      + +> Mailinglist:
      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06/raw.md b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f2fd82009eeaf1f8c19ddbad3fb1bf9be6d8eaee --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06/raw.md @@ -0,0 +1,55 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 06/07/2023 + +### Attendees + +| Companies | Attendees | +| --------- | --------- | +| Telefónica | Jesús Peña, Christian Duran | +| LibertyGlobal | George Haddad | + +
      + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +
      + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +
      + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
    23. Current project status: 2 open issues and no ongoing PRs.
    24. Issue 44 "Generation of release v0.2.0" has been CLOSED. Release [v0.2.0](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/v0.2.0) is now available.
    25. Issue #41 "WiFi QoS Mappings" has been CLOSED in view of the comments provided and the fact that there are no further objections.
    26. Issue #39 "Generation of release v1.0.0" is ongoing. From release v0.2.0, work will begin to generate the first stable API version v1.0.0 by contributing with the API test cases definition.
    27. New Issue #46 "Add option to apply QoD to subnets" | +| **Open Issues** | | +| | [#39](https://github.com/camaraproject/HomeDevicesQoD/issues/39) "Generation of release v1.0.0"
      Issue to validate and meet API readiness requirements to generate a first stable API release v1.0.0 from v0.2.0. No further functionality will be added to the API.
      • The requirement to fulfill step 5 ("API test cases and documentation") of the API Readiness checklist has been agreed in issue [#61](https://github.com/camaraproject/WorkingGroups/issues/61) of Commonalities. It has been confirmed that it is good enough to provide the ".feature" file.
      | +| | ~~[#41](https://github.com/camaraproject/HomeDevicesQoD/issues/41) "WiFi QoS Mappings"~~
      CLOSED in view of the comments provided and the fact that there are no further objections.
      The current proposal is based on the DSCP value set in the user's home router to control the QoS behaviour of the target home device's IP traffic. And it has been defined the "service class" concept on top of DSCP to provide a developer-friendly design following RFC4594 recommendations. So existing documented service class mapping to DSCP should be sufficient. | +| | ~~[#44](https://github.com/camaraproject/HomeDevicesQoD/issues/44) "Generation of release v0.2.0"~~
      CLOSED
      Addressed in PR [#45](https://github.com/camaraproject/HomeDevicesQoD/pull/45) which has been already merged. Release [v0.2.0](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/v0.2.0) is now available. | +| **New Issues** | | +| | [#46](https://github.com/camaraproject/HomeDevicesQoD/issues/46) "Add option to apply QoD to subnets"
      Open by Cablelabs (Randy Levensalor), it is intended to suggest an API enhancement to apply QoD to home subnets.
      This would be a new functionality, so formal procedure through GSMA OGW Product WS must be followed since GSMA is the one that manages priorities at the product level.
      From Telefónica perspective, suggested feature is probably more appropriate for an internal Operator application, where the user has a "control panel" or similar to manage their home network resources, devices and configurations (including subnets). But in the CAMARA context, where Operator exposes APIs to third party developers, the subnet information may not be known/accessible to the developer (exposed information is limited).| +| **AOB** | | +| |
    28. Next Home Devices QoD community call on July 20th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create PR to provide the ".feature" file as the API test cases definition. + +
      + +> Mailinglist:
      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/marked/HomeDevicesQoD/documentation/SupportingDocuments/README/raw.md b/marked/HomeDevicesQoD/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..220f01caa5a015a6cfd54e60ac74769669ec4546 --- /dev/null +++ b/marked/HomeDevicesQoD/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/marked/InHomeDeviceManagement/README/raw.md b/marked/InHomeDeviceManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f3b732b8c738c85791951316446a9fb59e3db34c --- /dev/null +++ b/marked/InHomeDeviceManagement/README/raw.md @@ -0,0 +1,42 @@ + + + + + + + + + +# InHomeDeviceManagement + +Sandbox API Repository to describe, develop, document, and test the InHomeDeviceManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQCxGw) + +## Scope + +* Service API(s) “InHomeDeviceManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: January 2026 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/EACpGw) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/InHomeDeviceManagement/code/API_definitions/README/raw.md b/marked/InHomeDeviceManagement/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/InHomeDeviceManagement/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/InHomeDeviceManagement/documentation/API_documentation/README/raw.md b/marked/InHomeDeviceManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/InHomeDeviceManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/InHomeDeviceManagement/documentation/SupportingDocuments/README/raw.md b/marked/InHomeDeviceManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/InHomeDeviceManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTDeviceManagement/README/raw.md b/marked/IoTDeviceManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1a6be22fc1447cece5d68dc943e3260a3a86f24e --- /dev/null +++ b/marked/IoTDeviceManagement/README/raw.md @@ -0,0 +1,43 @@ + + + + + + + + + +# IoTDeviceManagement + +Sandbox API Repository to describe, develop, document, and test the IoT Device Management Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/boCeBQ) + +## Scope + +* Service API(s) “IoTDeviceManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * manage communication functions, like activation and deactivation of voice, SMS, data services, and specific APNs, ensuring precise traffic control to prevent overload. + * manage device subscription state, perform operations such as adding, activating, suspending, restoring, deactivating, and deleting IoT cards. + * support real-time monitoring, provide visibility into the status of IoT cards, enabling continuous supervision and efficient control of service usage and status. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Tuesday, 13:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99489769217?password=b970b062-a3ef-4a58-95ed-2b15610d84fb) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/p4CgBQ) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/IoTDeviceManagement/code/API_definitions/README/raw.md b/marked/IoTDeviceManagement/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/IoTDeviceManagement/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/IoTDeviceManagement/documentation/API_documentation/README/raw.md b/marked/IoTDeviceManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTDeviceManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTDeviceManagement/documentation/SupportingDocuments/README/raw.md b/marked/IoTDeviceManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTDeviceManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTNetworkOptimization/README/raw.md b/marked/IoTNetworkOptimization/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6859b9314094db47f909f010745fa86a86a9da29 --- /dev/null +++ b/marked/IoTNetworkOptimization/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# IoTNetworkOptimization + +Sandbox API Repository to describe, develop, document, and test the IoTNetworkOptimization Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYCzBw) +* [Provider Implementation](https://github.com/camaraproject/IoTNetworkOptimization_PI) + +## Scope + +* Service API(s) “IoTNetworkOptimization” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * activate network features for that specific fleet of IoT devices, e.g., energy saving features. +* Describe, develop, document, and test the API(s) +* Started: April 2025 + + + + + +## Release Information + +> [!NOTE] +> This repository has only pre-release versions available yet. Pre-releases are for testing and may change before public release. + +* **PREVIEW**: The latest pre-release is [r1.1](https://github.com/camaraproject/IoTNetworkOptimization/releases/tag/r1.1) (alpha), with the following API versions: + * **iot-network-optimization v0.1.0-alpha.1** + [[YAML]](https://github.com/camaraproject/IoTNetworkOptimization/blob/r1.1/code/API_definitions/iot-network-optimization.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/IoTNetworkOptimization/r1.1/code/API_definitions/iot-network-optimization.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/IoTNetworkOptimization/r1.1/code/API_definitions/iot-network-optimization.yaml) +* For changes see [CHANGELOG.md](https://github.com/camaraproject/IoTNetworkOptimization/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Wednesday 10:00 AM - 11:00 AM UTC (12:00 PM -13:00 PM CEST): [wiki Calandar](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi?view=week) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/T4CzBw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/IoTNetworkOptimization/code/API_definitions/README/raw.md b/marked/IoTNetworkOptimization/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/IoTNetworkOptimization/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/IoTNetworkOptimization/code/API_definitions/iot-network-optimization/raw.md b/marked/IoTNetworkOptimization/code/API_definitions/iot-network-optimization/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5c1cd755de172d69a00632583524fb4507ee3217 --- /dev/null +++ b/marked/IoTNetworkOptimization/code/API_definitions/iot-network-optimization/raw.md @@ -0,0 +1,1075 @@ +# iot-network-optimization + +```yaml +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: IoT Network Optimization API + description: | + ## Overview + The IoT Network Optimization API provides the API Consumer with the + capabilities of activating IoT-specific features for a fleet of devices. + ## Introduction + The scenario a Service Provider that partners with a Telco Operator to + deploy IoT devices (e.g., sensors, trackers) across the Telco’s nationwide + cellular network. + To ensure prolonged device battery life and operational efficiency, the + Service Provider seeks to activate power-saving configurations for its IoT + fleet during periods of low activity or based on predefined thresholds. + The Service Provider’s management system invokes the IoT Network + Optimization API to dynamically adjust network connectivity parameters. + This includes optimizing data transmission intervals, reducing signal + strength during idle phases, and scheduling sleep cycles for devices + without disrupting critical service functionality. The API evaluates + network conditions, device locations, and application requirements to apply + energy-efficient settings while maintaining guaranteed quality-of-service + levels. By leveraging the API, the Provider ensures IoT devices consume + minimal power during operation, significantly extending battery lifetimes + and reducing energy costs. The optimization accounts for both device-level + energy savings and reduced overhead on the Telco’s network infrastructure + (e.g., lower RAN utilization during sleep cycles). Clients benefit from + uninterrupted service with no manual + intervention, aligning sustainability goals with operational reliability.\ + \ + **Example use case and flow:**\ + \ + [**Service**](https://github.com/camaraproject/\ + IoTNetworkOptimization/blob/main/documentation/API_documentation/\ + IoT_Network_Optimization_UserStory_UseCase_1.md)\ + \ + **The main elements of the IoT Network Optimization API are:**\ + \ + **PowerSavingRequest:** + Provides to the API Producer the intention of a enabling or disabling power + saving features for a specific set of IoT devices.\ + \ + **PowerSavingResponse:** + Provides to the API Consumer the status of the power-saving feature + activation based on the related transaction.\ + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details on how + an API consumer requests an access token. Please refer to Identify and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile.\ + \ + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation.\ + \ + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + ## API Documentation + ## Details + The IoT Network Optimization API provides the API Consumer with the + capability to activate and manage IoT-specific network features for a fleet + of connected devices. The API enables optimized power consumption + transmission by leveraging network-level configurations tailored for IoT + deployments. + + The IoT API allows an IoT Service Provider to dynamically adjust network + parameters to optimize device performance and reduce operational overhead. + The IoT API Consumer (typically the IoT Service Provider or a third-party + management system) invokes the API with identifiers for the target IoT + devices. The API then applies the requested optimizations, such as enabling + low-power modes for battery-operated sensors. + + By using the IoT Network Optimization API, Service Providers can ensure + their IoT deployments operate at peak efficiency extending device battery + life and improving overall service reliability. + + The IoT Network Optimization API is an intent based API. + \ + The IoT Network Optimization API supports the following Intent: + - Intent1: I would like to activate power-saving features for my IoT + devices during a specified period. + + The inputs for the above intent are: + - IoT devices (e.g., device identifiers like IPs or SIM phone number) + - power-saving desired status + - time frame (e.g., start/end timestamps) + + The output for the above intent are: + - activation status (success/failure per device or group) + - transaction ID for tracking + + The related endpoint is: + - Intent: /features/power-saving + + ## Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guidelines`. + + Please refer to [CAMARA_common.yaml]({link_to_release}/CAMARA_common.yaml) + for a complete list of error responses. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + ## FAQ's + (FAQs will be added in a later version of the documentation) + ## Release Notes + First draft for the IoT Network Optimization API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/IoTNetworkOptimization +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/iot-network-optimization/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root for the IoT Network Optimization API +security: + - notificationsBearerAuth: [] +tags: + - name: Power Saving + description: Enable/Disable power-saving features. +############################################################################ +# Paths # +############################################################################ +paths: + /features/power-saving: + post: + tags: + - Power Saving + summary: Activate or de-activate power-saving features for IoT devices + operationId: activatePowerSaving + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - oAuth2: + - 'iot-management:power-saving:write' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingRequest' + responses: + "202": + description: Power-saving feature request accepted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingResponse' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "501": + $ref: "#/components/responses/Generic501" + callbacks: + onTransactionCompleted: + $ref: "#/components/callbacks/onTransactionCompleted" + /features/power-saving/transactions/{transactionId}: + get: + parameters: + - name: transactionId + in: path + required: true + schema: + $ref: '#/components/schemas/TransactionId' + - $ref: '#/components/parameters/x-correlator' + tags: + - Power Saving + summary: Get status of a transaction for power-saving features + operationId: getPowerSaving + security: + - oAuth2: + - 'iot-management:power-saving:read' + responses: + "200": + description: Power-saving features activated successfully + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingResponse' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "501": + $ref: "#/components/responses/Generic501" + +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + oAuth2: + type: oauth2 + description: This API uses OAuth 2 + [More info](https://api.example.com/docs/auth) + flows: + clientCredentials: + tokenUrl: 'https://example.com/oauth/token' + scopes: + 'iot-management:power-saving:read': + Grants access to read-only data in the Power Saving resources + 'iot-management:power-saving:write': + Grants write access to the Power Saving resources + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onTransactionCompleted: + # when data is sent, it will be sent to the callback url provided + "{$request.body#/subscriptionRequest/sink}": + post: + summary: Provides back the result of the enabling operations + description: | + once the system has request to enable power-settings for all + the devices it collects the results and provides it back to + the API Consumer + operationId: IoTNetworkOptimizationNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the operation results + required: true + content: + application/cloudevents+json: + schema: + allOf: + - $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.iot-network-optimization-notification.v1.power-saving" + specversion: "1.0" + datacontenttype: "application/json" + data: + activationStatus: + - device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + status: "pending" + transactionId: "string" + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + ############################################################################ + # Resources # + ############################################################################ + schemas: + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 2 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.iot-network-optimization-notification.v1.power-saving + - org.camaraproject.iot-network-optimization-notification.v1.power-saving.error + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.iot-network-optimization-notification.v1.power-saving + - org.camaraproject.iot-network-optimization-notification.v1.power-saving.error + PowerSavingRequest: + type: object + required: + - devices + - enabled + - subscriptionRequest + properties: + devices: + type: array + items: + $ref: '#/components/schemas/Device' + description: Device IDs or group identifiers + enabled: + type: boolean + timePeriod: + required: + - startDate + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. + If not included, then the period has no ending date. + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required in + CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.iot-network-optimization-notification.v1.power-saving: "#/components/schemas/CloudEventPowerSaving" + org.camaraproject.iot-network-optimization-notification.v1.power-saving.error: "#/components/schemas/CloudEventError" + CloudEventPowerSaving: + description: provides back the power saving operation result. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + $ref: "#/components/schemas/PowerSavingResponse" + + CloudEventError: + description: Error notification for a power saving report request. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + transactionId: + type: string + format: uuid + description: Transaction identifier allocated for enabling/disabling IoT + features + required: + - transactionId + + PowerSavingResponse: + type: object + properties: + activationStatus: + type: array + items: + $ref: '#/components/schemas/DeviceStatus' + transactionId: + type: string + + DeviceStatus: + type: object + properties: + device: + $ref: '#/components/schemas/Device' + status: + type: string + enum: [pending, in-progress, success, failed] + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device + identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the MNO might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible + across different MNOs. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In + mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to + E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile + network. In 3GPP terminology, it corresponds to the GPSI formatted with + the External Identifier ({Local Identifier}@{Domain Identifier}). + Unlike the telephone number, the network access identifier is not + subjected to portability ruling in force, and is individually managed + by each operator. + type: string + example: "123456789@domain.com" + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is not + in use) then the same address should be specified for both + publicAddress and privateAddress. + If NAT64 is in use, the device should be identified by its publicAddress + and publicPort, or separately by its allocated IPv6 address (field + ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + TransactionId: + type: string + format: uuid + description: Transaction identifier allocated for enabling/disabling IoT + features + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Responses # + ############################################################################ + ErrorInfo: + description: error information + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: | + Request cannot be authenticated and a new authentication is + required + value: + status: 401 + code: UNAUTHENTICATED + message: | + Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - UNKNOWN_APPLICATION_IDENTIFIER + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Application Identifier unknown + value: + status: 404 + code: UNKNOWN_APPLICATION_IDENTIFIER + message: the target application is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + description: Device already in the requested state or conflicting operation in progress + value: + status: 409 + code: CONFLICT + message: The device is already in the requested power-saving state or a conflicting operation is in progress. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: the Application Identifier is not included in the + request + value: + status: 422 + code: MISSING_IDENTIFIER + message: unspecified Application Identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code + should be avoided as far as possible to get the objective + to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. +``` diff --git a/marked/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1/raw.md b/marked/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e187f8897b4c66b1e70d75ecbb344b0871f7aa04 --- /dev/null +++ b/marked/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1/raw.md @@ -0,0 +1,11 @@ + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service Provider partners with a Telco Operator to deploy IoT devices (e.g., sensors, trackers) across the Telco’s nationwide cellular network. To ensure prolonged device battery life and operational efficiency, the Service Provider seeks to activate power-saving configurations for its IoT fleet during periods of low activity or based on predefined thresholds. The Service Provider’s management system invokes the IoT Network Optimization API to dynamically adjust network connectivity parameters. This includes optimizing data transmission intervals, reducing signal strength during idle phases, and scheduling sleep cycles for devices without disrupting critical service functionality. The API evaluates network conditions, device locations, and application requirements to apply energy-efficient settings while maintaining guaranteed quality-of-service levels. By leveraging the API, the Provider ensures IoT devices consume minimal power during operation, significantly extending battery lifetimes and reducing energy costs. The optimization accounts for both device-level energy savings and reduced overhead on the Telco’s network infrastructure (e.g., lower RAN utilization during sleep cycles). Clients benefit from uninterrupted service with no manual intervention, aligning sustainability goals with operational reliability.| M | +|Roles, Actor(s) and scope|• Service Provider: role of IoT Network Optimization API consumer
      API Provider: role of IoT Network Optimization API provider
      • Operator Platform ([EdgeCloud/documentation/SupportingDocuments/Edge terminology/edge_terminology.md at main · camaraproject/EdgeCloud](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/Edge%20terminology/edge_terminology.md)): role of Service host
      • End User: both Teclo Operator's subscribers and Service Provider customer, role of Service consumer
      • Scope: Computing Services (OGW Taxonomy)| M | +|NF Requirements|NA| O | +|Pre-conditions|• The Service Provider has a fleet of IoT devices
      • The IoT devices are connected to the Operator network.| M | +|Begins when|The API Consumer invokes the IoT Network Optimization API to set power-saving features for a fleet of IoT devices with a specific configuration.| M | +|Step 2|The API Provider returns a transaction identifier to check the status of the request. | M| +|Step 3|The API Provider invokes a callback to the API Consumer to notifiy the final status of the requested operation. | M | +|Post-conditions|The Service Provider devices can leverege an optimized network configuration to save power. | M | diff --git a/marked/IoTNetworkOptimization/documentation/API_documentation/README/raw.md b/marked/IoTNetworkOptimization/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTNetworkOptimization/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist/raw.md b/marked/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..23e1198c0af04d93a3781921cbd075cd3b0e8c5f --- /dev/null +++ b/marked/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for iot-network-optimization v0.1.0-alpha.1 in r1.1 + +| Nr | API release assets | alpha | release-candidate | initial
      public | stable
      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/iot-network-optimization.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | N | not fully checked | +| 3 | Guidelines from ICM applied | O | M | M | M | N | not fully checked | +| 4 | API versioning convention applied | M | M | M | M | Y | 0.1.0-alpha.1 | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/iot-network-optimization.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/iot-network-optimization-power-saving.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.1 | +| 11 | Change log updated | M | M | M | M | Y | | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AQCGDg) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/IoTNetworkOptimization/documentation/SupportingDocuments/README/raw.md b/marked/IoTNetworkOptimization/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTNetworkOptimization/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTSIMFraudPrevention/README/raw.md b/marked/IoTSIMFraudPrevention/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ed0755cca7b65fb8fefa3a9040069beb74760182 --- /dev/null +++ b/marked/IoTSIMFraudPrevention/README/raw.md @@ -0,0 +1,41 @@ + + + + + + + + + +# IoTSIMFraudPrevention + +Sandbox API Repository to describe, develop, document, and test the IoT SIM Fraud Prevention Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/xwKaBQ) + +## Scope + +* Service API(s) “IoTSIMFraudPrevention” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * manage device-card binding, includes bindng/unbinding imei to the card, when the imei is not match with the bind information, operator will block the network, when the imei is match, resume the network.. + * manage device-area binding, includes binding/unbinding area to the card, when the area is not match with the bind information, operator will block the network, when the area is match, resume the network. + * query risk control information related to IoT SIM cards, includes machine-card binding and region restriction. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Every 2 weeks on Wednesdays at 9:00 UTC (start from April 30th, 2025) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92159554978?password=c5c63329-3b55-4fe0-94d9-9091c51f2ef9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/GwCfBQ) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/IoTSIMFraudPrevention/code/API_definitions/README/raw.md b/marked/IoTSIMFraudPrevention/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/IoTSIMFraudPrevention/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions/raw.md b/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1e2613ceec105fe6b8de625327826becb12432f3 --- /dev/null +++ b/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions/raw.md @@ -0,0 +1,1540 @@ +# iot-sim-fraud-prevention-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: IoT SIM Fraud Prevention Subscriptions + description: | + API to subscribe to events related to SIM card binding and regional restrictions. + + # Introduction + This API allows enterprise customers to subscribe to risk control information about IoT SIM cards. + When a bound device changes IMEI or moves in/out of a restricted area, a notification is sent to the registered callback endpoint. + + # Relevant terms and definitions + * **SIM card**: IoT network card (subscriber identity module). + * **Binding**: mechanism linking a SIM card to a specific terminal device (IMEI) or area. + * **Device**: any physical entity that can connect to a network. + * **IMEI**: International Mobile Equipment Identity. + + # API Functionality + The API provides endpoints to manage subscriptions: + - `POST /subscriptions` – create a subscription. + - `GET /subscriptions/{subscriptionId}` – retrieve a subscription. + - `DELETE /subscriptions/{subscriptionId}` – delete a subscription. + + # Notifications + When a subscribed event occurs, the server sends a `POST` request to the `sink` URL provided by the subscriber. + The notification payload conforms to the CloudEvents specification. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification MAY not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.7.0 +externalDocs: + description: CAMARA API Design Guidelines + url: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design/API-design.md +servers: + - url: "{apiRoot}/iot-sim-fraud-prevention-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +paths: + /subscriptions: + post: + tags: + - Subscription sim card fraud prevention + summary: Subscribe to IMEI or area change events + description: | + Create a subscription to receive notifications when the IMEI of a device changes or when it enters/leaves a restricted area. + operationId: subscribeFraudPrevention + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: Subscription For One Device By IPv4 Address + description: Use the IPv4 address of a device for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_IPV6_ADDRESS: + summary: Subscription For One Device By IPV6 Address + description: Use the IPv6 address of a device for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_PHONE_NUMBER: + summary: Subscription For One Device By Device Number + description: Use a device's phone number for subscription operation + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + phoneNumber: "+123456789" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: Subscription For One Device By Network Access Identification + description: Use a device's network access identifier for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + networkAccessIdentifier: "123456789@domain.com" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important note: This endpoint will be implemented by API users. + Whenever an IMEI or area change event occurs, the server will call this endpoint. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/NotificationEvent" + examples: + IMEI_CHANGE: + description: The trigger event when the device IMEI has changed + value: + specversion: "1.0" + source: "https://api.example.com" + id: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + type: "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + datacontenttype: "application/json" + time: "2023-03-22T05:40:23.682Z" + data: + subscriptionId: "987654321" + imei: "35-209900-176148-1" + device: + phoneNumber: "+123456789" + AREA_CHANGE: + description: The trigger event when the device area has changed + value: + specversion: "1.0" + source: "https://api.example.com" + id: "b4333c46-49c0-4f62-80d7-f0ef930f1c47" + type: "org.camaraproject.iot-sim-fraud-prevention.v0.area-change" + datacontenttype: "application/json" + time: "2023-03-22T05:41:23.682Z" + data: + subscriptionId: "987654321" + area: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + device: + phoneNumber: "+123456789" + responses: + "204": + description: Successful notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/CallbackBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "410": + $ref: "#/components/responses/Callback410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Created (Successful creation of subscription). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: | + The result of subscription machine card binding or region restriction change events + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscribeFraudPreventionResponseAsync" + examples: + RESULT_SUBSCRIPTION_ID: + summary: subscription result + description: | + The result of subscription device's IMEI or region change + value: + subscriptionId: "1119920371" + "400": + $ref: "#/components/responses/SubscribeBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Subscribe422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:subscribe" + + get: + tags: + - Subscription management + summary: List subscriptions + description: Retrieve a list of existing subscriptions. + operationId: listSubscriptions + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: List of subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + maxItems: 1000 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:read" + + /subscriptions/{subscriptionId}: + get: + tags: + - Subscription management + summary: Get subscription details + description: Retrieve the details of an existing subscription. + operationId: getSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: subscriptionId + in: path + required: true + schema: + type: string + description: Identifier of the subscription. + responses: + "200": + description: Subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:read" + + delete: + tags: + - Subscription management + summary: Delete subscription + description: Delete an existing subscription. After deletion, no further notifications will be sent. + operationId: deleteSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: subscriptionId + in: path + required: true + schema: + type: string + description: Identifier of the subscription. + responses: + "204": + description: Subscription successfully deleted. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed asynchronously. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:delete" + +components: + securitySchemes: + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + description: | + Bearer token authentication for the callback endpoint. The token format is determined + by `sinkCredential.credentialType` in the subscription request. + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + description: Correlation id for the request + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + + # ---------- Notification ---------- + CloudEvent: + type: object + description: | + CloudEvents 1.0 specification envelope. + This schema is the stable base for all CAMARA event notifications. + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + maxLength: 256 + description: Identifier of this event, unique within the source context. + source: + $ref: "#/components/schemas/Source" + type: + type: string + maxLength: 512 + description: | + Identifies the event type. CAMARA APIs use reverse-DNS notation: + `org.camaraproject...` + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload. Structure is defined by each concrete event schema. + time: + $ref: "#/components/schemas/DateTime" + + Source: + type: string + format: uri-reference + minLength: 1 + maxLength: 2048 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://api.example.com" + + DateTime: + type: string + format: date-time + maxLength: 64 + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + # ───────────────────────────────────────────────────────────────────────── + # API-specific notification event group + # ───────────────────────────────────────────────────────────────────────── + + ApiNotificationEvent: + description: | + API-specific notification event group. + Extends the CloudEvent envelope and constrains `type` to the set of + event types defined by this API project. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + $ref: "#/components/schemas/ApiEventType" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.iot-sim-fraud-prevention.v0.imei-change: "#/components/schemas/ImeiChangeEvent" + org.camaraproject.iot-sim-fraud-prevention.v0.area-change: "#/components/schemas/AreaChangeEvent" + + ApiEventType: + type: string + description: | + Enum of API-specific event type strings for this API project. + The reverse-DNS prefix `org.camaraproject.iot-sim-fraud-prevention` makes each value + globally unique. + enum: + - org.camaraproject.iot-sim-fraud-prevention.v0.imei-change + - org.camaraproject.iot-sim-fraud-prevention.v0.area-change + + ImeiChangeEvent: + description: Event structure for IMEI change notification + allOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ImeiChangeEventData" + + ImeiChangeEventData: + type: object + required: + - subscriptionId + - imei + - device + properties: + subscriptionId: + type: string + description: The ID of the subscription that triggered this notification + example: "987654321" + imei: + type: string + description: The new IMEI of the device + example: "35-209900-176148-1" + device: + $ref: "#/components/schemas/Device" + + AreaChangeEvent: + description: Event structure for area change notification + allOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaChangeEventData" + + AreaChangeEventData: + type: object + required: + - subscriptionId + - area + - device + properties: + subscriptionId: + type: string + description: The ID of the subscription that triggered this notification + example: "987654321" + area: + $ref: "#/components/schemas/Area" + device: + $ref: "#/components/schemas/Device" + + # ───────────────────────────────────────────────────────────────────────── + # Subscription lifecycle event group (Commonalities-owned) + # ───────────────────────────────────────────────────────────────────────── + + SubscriptionLifecycleEvent: + description: | + Subscription lifecycle event group, common to all CAMARA APIs that + support explicit subscriptions. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + $ref: "#/components/schemas/SubscriptionLifecycleEventType" + discriminator: + propertyName: type + mapping: + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + SubscriptionLifecycleEventType: + type: string + description: | + Enum of subscription lifecycle event type strings. + enum: + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-started + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-updated + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-ended + + EventSubscriptionStarted: + description: event structure for event subscription started + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + type: string + maxLength: 512 + description: Description of subscription initiation + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + type: string + maxLength: 512 + description: Description of subscription update + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + maxLength: 512 + description: Description of subscription termination + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester with credential type `ACCESSTOKEN`) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + # ───────────────────────────────────────────────────────────────────────── + # Callback union (API project-owned) + # ───────────────────────────────────────────────────────────────────────── + + NotificationEvent: + description: | + Union of all valid notification event groups at the callback endpoint. + oneOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + + # ---------- Subscription schemas ---------- + Subscription: + description: Represents an event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + maxLength: 2048 + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered. + example: "https://endpoint.example.com/sink" + types: + description: Event types eligible to be delivered. + type: array + minItems: 1 + maxItems: 1 + items: + type: string + example: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + config: + $ref: "#/components/schemas/Config" + id: + type: string + description: Unique identifier of the subscription. + example: "1119920371" + startsAt: + type: string + format: date-time + description: Date when the subscription begins. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: Date when the subscription expires (if applicable). + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: Current status of the subscription. + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: Response for a subscription request managed asynchronously + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + maxLength: 256 + description: The unique identifier of the subscription + example: "1119920371" + + SubscribeFraudPreventionResponseAsync: + description: Response for an asynchronous subscription creation. + type: object + properties: + subscriptionId: + type: string + description: The unique identifier of the subscription. + example: "1119920371" + required: + - subscriptionId + + SubscribeFraudPreventionRequest: + description: Request to create a subscription. + type: object + required: + - sink + - protocol + - config + - types + properties: + config: + $ref: "#/components/schemas/Config" + types: + description: Event types to subscribe to (only one allowed per subscription). + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/ApiEventType" + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + maxLength: 2048 + pattern: ^https:\/\/.+$ + description: The callback URL where notifications will be sent. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Config: + description: Configuration parameters for the subscription. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: "2023-01-17T13:18:23.682Z" + subscriptionMaxEvents: + type: integer + minimum: 1 + example: 5 + initialEvent: + type: boolean + + SubscriptionDetail: + description: Details specific to the subscribed events. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + required: + - device + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Delivery protocol (only HTTP is currently allowed). + example: "HTTP" + + # ---------- Sink credentials ---------- + SinkCredential: + type: object + description: Authentication/authorization information for the callback sink. + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - PRIVATE_KEY_JWT + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + PRIVATE_KEY_JWT: "#/components/schemas/PrivateKeyJWTCredential" + required: + - credentialType + + PlainCredential: + type: object + description: Plain username/password credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + type: string + secret: + type: string + + AccessTokenCredential: + type: object + description: Bearer token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + type: string + accessTokenExpiresUtc: + type: string + format: date-time + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + PrivateKeyJWTCredential: + type: object + description: Use PRIVATE_KEY_JWT to get an access token. The authorization server information needed for this type of sink credential (token endpoint, client ID, JWKS URL) is shared upfront between the client and the CAMARA entity. This type of credential is to be used by clients that have an authorization server. + allOf: + - $ref: "#/components/schemas/SinkCredential" + + # ---------- Device identification (same as main API) ---------- + Device: + description: End-user device identification. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + + # ---------- Geographic area (used in AREA_CHANGE notification) ---------- + Area: + description: Geographic area. + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + point: + $ref: "#/components/schemas/Point" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + enum: + - CIRCLE + + Circle: + description: Circular area. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + minimum: 1 + maximum: 200000 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + # ---------- Error ---------- + ErrorInfo: + description: Common error schema. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + code: + type: string + message: + type: string + + # ---------- Protocol-specific subscription schemas ---------- + HTTPSubscriptionRequest: + description: Subscription request for HTTP-based event delivery. + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + description: Subscription resource returned for HTTP-based event delivery. + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + description: HTTP protocol settings for event delivery. + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + additionalProperties: + type: string + maxLength: 512 + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + # Other protocol schemas (MQTT, AMQP, etc.) would be defined here if needed + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + maxLength: 256 + description: MQTT topic name + qos: + type: integer + format: int32 + minimum: 0 + maximum: 2 + description: Quality of Service level (0, 1, or 2) + retain: + type: boolean + expiry: + type: integer + format: int32 + minimum: 0 + maximum: 2147483647 + description: Message expiry interval in seconds + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + maxLength: 512 + linkName: + type: string + maxLength: 256 + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + maxLength: 1024 + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + maxLength: 249 + partitionKeyExtractor: + type: string + maxLength: 512 + clientId: + type: string + maxLength: 256 + ackMode: + type: integer + format: int32 + minimum: 0 + maximum: 2 + description: Acknowledgment mode (0=no ack, 1=leader ack, 2=all replicas ack) + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + maxLength: 256 + description: NATS subject + required: + - subject + + # ---------- Responses ---------- + responses: + SubscribeBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_SINK + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient Types Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "SubscriptionType must be specified" + Invalid Sink Value: + value: + status: 400 + code: INVALID_SINK + message: "The sink field must be an accessible client address in order to notify the other end when an event occurs" + Invalid Protocol Value: + value: + status: 400 + code: INVALID_PROTOCOL + message: "The value of Protocol can only be HTTP, MQTT3, MQTT5, AMQP, NATS, KAFKA" + + CallbackBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + Insufficient Id Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Id must be specified" + Insufficient Type Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Type must be specified" + Insufficient Time Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Time must be specified" + Insufficient Data Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Data must be specified" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Subscribe422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + + Callback410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: + Access to the target resource is no longer available. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. +``` diff --git a/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention/raw.md b/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9b62c99c8ee6ac3277763069217041a28a406903 --- /dev/null +++ b/marked/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention/raw.md @@ -0,0 +1,1145 @@ +# iot-sim-fraud-prevention + +```yaml +openapi: 3.0.3 +info: + title: IoT SIM Fraud Prevention + description: | + API for SIM card binding/unbinding and regional restriction management. + + # Introduction + This API provides operations to manage security mechanisms for IoT SIM cards: + - **Bind**: associate a SIM card with a specific device (IMEI) or restrict its operation to a geographic area. + - **Unbind**: remove an existing binding or area restriction. + - **Query**: retrieve the current binding status or area restriction for a device. + + When a device attempts to use the network, the operator checks the binding/restriction. + If the IMEI reported does not match the bound one, or the device location is outside the allowed area, + network services are automatically blocked. + + # Relevant terms and definitions + * **SIM card**: IoT network card (subscriber identity module). + * **Binding**: mechanism linking a SIM card to a specific terminal device (IMEI) to prevent misuse. + * **Device**: any physical entity that can connect to a network. + * **IMEI**: International Mobile Equipment Identity, a unique 15-digit identifier for mobile devices. + + # API Functionality + The API exposes three endpoints: + - `POST /bind` – bind IMEI or area to a card. + - `POST /unbind` – unbind IMEI or area from a card. + - `POST /query` – query binding/restriction status. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification MAY not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.7.0 +externalDocs: + description: CAMARA API Design Guidelines + url: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design/API-design.md +servers: + - url: "{apiRoot}/iot-sim-fraud-prevention/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +paths: + /bind: + post: + tags: + - Bind sim card fraud prevention + summary: Bind device IMEI or area restrictions + description: Associate a SIM card with a specific IMEI or restrict it to a geographic area. + operationId: bindDeviceImei + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/BindDeviceImeiRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: bind imei For One Device By IPv4 Address + description: Use the IPv4 address of a device for binding operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + bindType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: bind imei For One Device By IPv6 Address + description: Use the IPv6 address of a device for binding operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + bindType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: bind imei For One Device By Phone Number + description: Use a device's number for binding operation + value: + device: + phoneNumber: "+123456789" + bindType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: bind imei For One Device By Network Access Identifier + description: Use a device's network access identifier for binding operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + bindType: "IMEIBIND" + INPUT_BIND_TYPE: + summary: bind imei For One Device By 3 Legged Token + description: Use a 3 Legged Token for binding operations (no device object needed) + value: + bindType: "IMEIBIND" + responses: + "200": + description: The result of binding the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BindDeviceImeiResponse" + examples: + BIND_SUCCESS: + summary: BOUND SUCCESSFULLY + description: The result of binding the device is successful + value: + bound: "TRUE" + BIND_FAIL: + summary: BOUND FAILED + description: The result of binding the device is a failure + value: + bound: "FALSE" + "400": + $ref: "#/components/responses/BindBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Bind422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:bind" + + /unbind: + post: + tags: + - Unbind sim card fraud prevention + summary: Unbind device IMEI or area restrictions + description: Remove an existing IMEI binding or area restriction from a device. + operationId: unBindDeviceImei + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/UnBindDeviceImeiRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: unbind imei For One Device By IPv4 Address + description: Use the IPv4 address of a device for unbinding operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + unBindType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: unbind imei For One Device By IPv6 Address + description: Use the IPv6 address of a device for unbinding operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + unBindType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: unbind imei For One Device By Phone Number + description: Use a device's number for unbinding operation + value: + device: + phoneNumber: "+123456789" + unBindType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: unbind imei For One Device By Network Access Identifier + description: Use a device's network access identifier for unbinding operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + unBindType: "IMEIBIND" + INPUT_UNBIND_TYPE: + summary: unbind imei For One Device By 3 Legged Token + description: Use a 3 Legged Token for unbinding operations (no device object needed) + value: + unBindType: "IMEIBIND" + responses: + "200": + description: The result of unbinding the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/UnBindDeviceImeiResponse" + examples: + UNBIND_SUCCESS: + summary: UNBOUND SUCCESSFULLY + description: The result of unbinding the device is successful + value: + unbound: "TRUE" + UNBIND_FAIL: + summary: UNBOUND FAILED + description: The result of unbinding the device is a failure + value: + unbound: "FALSE" + "400": + $ref: "#/components/responses/UnbindBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Unbind422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:unbind" + + /query: + post: + tags: + - Query card fraud prevention + summary: IoT SIM Fraud Prevention Query + description: Retrieve the current IMEI binding status or area restriction for a device. + operationId: query + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/QueryRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: query For One Device By IPv4 Address + description: Use the IPv4 address of a device for query operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + queryType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: query For One Device By IPv6 Address + description: Use the IPv6 address of a device for query operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + queryType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: query For One Device By Phone Number + description: Use a device's number for query operation + value: + device: + phoneNumber: "+123456789" + queryType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: query For One Device By Network Access Identifier + description: Use a device's network access identifier for query operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + queryType: "IMEIBIND" + INPUT_UNBIND_TYPE: + summary: query For One Device By 3 Legged Token + description: Use a 3 Legged Token for query operations (no device object needed) + value: + queryType: "IMEIBIND" + responses: + "200": + description: The result of query the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/QueryFraudPreventionResponse" + examples: + AREA_LIMIT_RESULT: + summary: AREALIMIT RESULT + description: The result of query sim card area limit + value: + areaLimit: + areaLimitStatus: "RESTRICTED" + limitArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + IMEI_BIND_RESULT: + summary: BINDIMEI RESULT + description: The result of query sim card imei bind + value: + imeiBind: + bindImei: "35-209900-176148-1" + bindStatus: "BOUND" + "400": + $ref: "#/components/responses/QueryBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Query422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:query" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + description: Correlation id for the request + example: "123e4567-e89b-12d3-a456-426614174000" + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + + # ---------- Bind / Unbind / Query common schemas ---------- + Device: + description: | + End-user device able to connect to a mobile network. + The developer can choose to provide one or more of the following identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + If multiple identifiers are provided, they MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription, formatted according to E.164 with a leading '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network (e.g., GPSI formatted as External Identifier). + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + Identification of a device using its IPv4 address. + At least one of `privateAddress` or `publicPort` must be provided together with `publicAddress`. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask. + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number. + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + A single IPv6 address identifying the device. + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + + # ---------- Bind ---------- + BindType: + type: string + description: The type of binding operation (IMEI or area limit). + enum: + - AREALIMIT + - IMEIBIND + + BindDeviceImeiRequest: + description: Request to bind IMEI or area limit to a device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + bindType: + $ref: "#/components/schemas/BindType" + required: + - bindType + + BindDeviceImeiResponse: + description: Response indicating whether the binding operation succeeded. + type: object + required: + - bound + properties: + bound: + type: string + description: "TRUE if binding succeeded, FALSE otherwise." + example: "TRUE" + + # ---------- Unbind ---------- + UnbindType: + type: string + description: The type of unbinding operation (IMEI or area limit). + enum: + - AREALIMIT + - IMEIBIND + + UnBindDeviceImeiRequest: + description: Request to unbind IMEI or area limit from a device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + unBindType: + $ref: "#/components/schemas/UnbindType" + required: + - unBindType + + UnBindDeviceImeiResponse: + description: Response indicating whether the unbinding operation succeeded. + type: object + required: + - unbound + properties: + unbound: + type: string + description: "TRUE if unbinding succeeded, FALSE otherwise." + example: "TRUE" + + # ---------- Query ---------- + QueryType: + type: string + description: The type of query (IMEI binding or area limit). + enum: + - AREALIMIT + - IMEIBIND + + QueryRequest: + description: Request to query the current status. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + queryType: + $ref: "#/components/schemas/QueryType" + required: + - queryType + + QueryFraudPreventionResponse: + description: Response containing the requested status. + type: object + properties: + areaLimit: + $ref: "#/components/schemas/AreaLimit" + imeiBind: + $ref: "#/components/schemas/ImeiBind" + + ImeiBind: + description: IMEI binding status and bound IMEI (if any). + type: object + properties: + bindImei: + $ref: "#/components/schemas/BindImei" + bindStatus: + $ref: "#/components/schemas/BindStatus" + + BindImei: + description: The IMEI currently bound to the SIM card (15 digits). + type: string + example: "35-209900-176148-1" + + BindStatus: + description: | + Status of the IMEI binding. + - `BOUND`: an IMEI is bound. + - `UNBOUND`: no IMEI is bound. + type: string + enum: + - BOUND + - UNBOUND + + AreaLimit: + description: Area restriction status and details of the restricted area. + type: object + properties: + limitArea: + $ref: "#/components/schemas/Area" + areaLimitStatus: + $ref: "#/components/schemas/AreaLimitStatus" + + AreaLimitStatus: + description: | + Current status of area restrictions. + - `RESTRICTED`: the device is currently restricted to a specific area. + - `UNRESTRICTED`: no area restriction is active. + type: string + enum: + - RESTRICTED + - UNRESTRICTED + + # ---------- Geographic area ---------- + Area: + description: Base schema for geographic areas. + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + point: + $ref: "#/components/schemas/Point" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: Type of the area. + enum: + - CIRCLE + + Circle: + description: A circular area defined by a center point and a radius. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + description: Radius in meters (minimum 1, maximum 200000). + minimum: 1 + maximum: 200000 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude). + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component (-90 to 90). + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component (-180 to 180). + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + # ---------- Error ---------- + ErrorInfo: + description: Common error schema. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code. + code: + type: string + description: Error code. + message: + type: string + description: Human-readable explanation. + + # ---------- Responses ---------- + responses: + BindBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient BindType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "BindType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid BindType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of bindType can only be IMEIBIND,AREALIMIT" + + UnbindBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient UnbindType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "UnbindType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid UnbindType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of unbindType can only be IMEIBIND,AREALIMIT" + + QueryBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient QueryType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "QueryType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid QueryType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of queryType can only be IMEIBIND,AREALIMIT" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Bind422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - UNNECESSARY_UNBIND_IMEI + - UNNECESSARY_UNBIND_AREALIMIT + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Unnecessary Unbind BINDIMEI: + description: The IMEI of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_IMEI + message: The current device imei has been unbound + Unnecessary Unbind AREALIMIT: + description: The area limit of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_AREALIMIT + message: The current device area limit has been unbound + + Unbind422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - UNNECESSARY_UNBIND_IMEI + - UNNECESSARY_UNBIND_AREALIMIT + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Unnecessary Unbind BINDIMEI: + description: The IMEI of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_IMEI + message: The current device imei has been unbound + Unnecessary Unbind AREALIMIT: + description: The area limit of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_AREALIMIT + message: The current device area limit has been unbound + + Query422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. +``` diff --git a/marked/IoTSIMFraudPrevention/documentation/API_documentation/README/raw.md b/marked/IoTSIMFraudPrevention/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTSIMFraudPrevention/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story/raw.md b/marked/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0811918280d6cefd536777c16325b893b1264e1c --- /dev/null +++ b/marked/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story/raw.md @@ -0,0 +1,10 @@ +# IoT SIM Fraud Prevention API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise customer managing IoT devices, I need to prevent SIM card fraud by binding SIM cards to specific devices (IMEI binding) and restricting their usage to specific geographic areas (area restrictions). This helps me ensure that my IoT SIM cards are only used on authorized devices in authorized locations, preventing unauthorized usage and potential fraud. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:Administrator, Customer:User
      **Actors:** Enterprise IoT administrators, IoT platform operators, security teams. The API handles both two-legged and three-legged access tokens for device identification.
      **Scope:**
      • Bind and unbind IMEI numbers to SIM cards
      • Set and remove geographic area restrictions
      • Query current binding and restriction status
      • Subscribe to notifications for IMEI or area changes
      • Receive real-time alerts when unauthorized changes occur
      | +| ***Pre-conditions*** |The preconditions are listed below:
      1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
      2. The Customer:BusinessManager has successfully subscribed to the IoT SIM Fraud Prevention product from the product catalog.
      3. The Customer:Administrator has onboarded the Customer:User to the platform.
      4. The Customer:User has obtained valid identifiers for the target IoT devices or will use three-legged access tokens for device identification.
      5. The enterprise has legitimate business needs for device binding and area restrictions for their IoT deployments.
      6. | +| ***Activities/Steps*** | **Starts when:**
        1. The customer identifies IoT devices that require fraud prevention measures

        **Main Operations:**
        2. The customer makes a POST request to `/bind` to establish IMEI binding or area restrictions for specific devices
        3. The customer makes a POST request to `/unbind` to remove existing bindings or restrictions when devices are decommissioned or relocated
        4. The customer makes a POST request to `/query` to check current binding and restriction status
        5. The customer makes a POST request to `/subscribe` to receive notifications when IMEI or area changes occur
        6. The system automatically blocks network services when unauthorized IMEI usage or area violations are detected

        **Ends when:**
        The IoT SIM cards are properly secured with appropriate bindings and restrictions, and the customer has visibility into the security status through queries and notifications. | +| ***Post-conditions*** | 1. For successful bind operations: The SIM card is bound to the specified IMEI or area, and network services will be blocked if unauthorized usage is detected.
        2. For successful unbind operations: The existing binding or restriction is removed, allowing the SIM card to be used on different devices or in different areas.
        3. For query operations: The current binding and restriction status is returned, providing visibility into the security configuration.
        4. For subscription operations: Notifications are sent to the specified callback URL when relevant changes occur.
        5. The system automatically enforces the configured security policies by blocking unauthorized usage.| +| ***Exceptions*** | Several exceptions might occur
        - Authentication failures: Invalid, missing, or expired access tokens
        - Authorization failures: Insufficient permissions or scope
        - Invalid inputs: Missing required parameters, invalid parameter values, or inconsistent device identifiers
        - Device not found: Provided device identifiers don't match any known devices
        - Unsupported operations: Attempting to unbind when no binding exists, or using unsupported identifier types
        - Rate limiting: Exceeding API quota or request rate limits
        - Network errors: Temporary service unavailability or callback endpoint issues| \ No newline at end of file diff --git a/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist/raw.md b/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7d6ed652068dafc37c1ad663f49b406d031debba --- /dev/null +++ b/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for api-name api-version in rx.y. + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](/code/API_definitions) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [relative link](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [relative link](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml (or [relative link](/documentation/API_documentation)) | +| 6 | User stories | O | O | O | M | Y | [relative link](/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/iot-sim-fraud-prevention-callback.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [relative link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | issue link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | see (1) | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/93979335/IoTSIMFraudPrevention) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: 1. Certified companies can be found on the GSMA Open Gateway Portal: https://open-gateway.gsma.com/ + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/README/raw.md b/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/IoTSIMFraudPrevention/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomer/README/raw.md b/marked/KnowYourCustomer/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a107c35ed1cfbab0067a99148b4fe439569ad44a --- /dev/null +++ b/marked/KnowYourCustomer/README/raw.md @@ -0,0 +1,55 @@ + + + + + + + + + +# KnowYourCustomer + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomer Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) + +* API wiki page: [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/BjPe) + + +> [!WARNING] +> After the CAMARA Spring25 meta release this repository has been separated into 3 individual repositories: +> - [KnowYourCustomerMatch](https://github.com/camaraproject/KnowYourCustomerMatch) +> - [KnowYourCustomerFill-in](https://github.com/camaraproject/KnowYourCustomerFill-in) +> - [KnowYourCustomerAgeVerification](https://github.com/camaraproject/KnowYourCustomerAgeVerification) +> +> This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + + +## Scope + +* Service APIs for “KnowYourCustomer” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * compare the information it (Service Provider, SP) has for a particular user with that on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. (KYC Match) + * request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. (KYC Fill-in) + * check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc. (KYC Age Verification) +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: September 2023 +* Incubating stage since: February 2025 + +## Release Information + +* Note: Please be aware that the project will have updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. For best results, use the latest available release + +* `NEW`:**The latest public release of CAMARA Know Your Customer is [r2.2](https://github.com/camaraproject/KnowYourCustomer/tree/r2.2)**. The Release Tag is [r2.2](https://github.com/camaraproject/KnowYourCustomer/releases/tag/r2.2). + - Contains the following API definitions **with inline documentation**: + - kyc-match: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-match.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-match.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-match.yaml&nocors) + - kyc-fill-in: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-fill-in.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-fill-in.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-fill-in.yaml&nocors) + - kyc-age-verification: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-age-verification.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-age-verification.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-age-verification.yaml&nocors) + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly, Tuesday, 09:00 CEST (07:00 UTC) (till October 27th 2024) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-kyc + * A message to the community of this Sub Project can be sent using diff --git a/marked/KnowYourCustomer/code/API_definitions/kyc-age-verification/raw.md b/marked/KnowYourCustomer/code/API_definitions/kyc-age-verification/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..25d1f841675c736365ef2ee731d466899f8de359 --- /dev/null +++ b/marked/KnowYourCustomer/code/API_definitions/kyc-age-verification/raw.md @@ -0,0 +1,511 @@ +# kyc-age-verification + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Age Verification + + description: | + + # Summary + This API provides the customer with the ability to check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. + + # API functionality + + The API defines one service endpoint: + + - `POST /verify` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and checks if the age of the subscriber is older than the age threshold in the request. + Additionally, as optional function, provides (1) if age check is done against another form of official identification or not (verifiedStatus), (2) an overall score of how certain is the response using both information provided in the request and information that the Operator holds(identityMatchScore), (3) an indicator on whether the subscription has any kind of content lock (contentLock) and (4) an indicator on whether the subscription has any kind of parental control activated (parentalControl). + + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). [Required only in case a 2-legged flow has been agreed between API Provider and API Consumer following CAMARA directives; otherwise, phoneNumber must not be included] + - `ageThreshold`: The age threshold from which the age of the user must be compared. [Required] + - any of `idDocument`, `name`, `givenName`, `familyName`, `middleNames`, `familyNameAtBirth`, `birthdate`, `email`; additional subscriber's information to be checked in order to confirm that the subscriber is the contract's owner [Optional] + - `includeContentLock` and `includeParentalControl`: These two flags allow the API Client to indicate that the corresponding response properties `contentLock` and `parentalControl` should be returned. Its implementation is optional for the API Provider, so in such cases, these parameters will be ignored. [Optional] + + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `ageCheck`: Indicate 'true' when the age of the user is the same age or older than the age threshold (age >= age threshold), and 'false' if not (age < age threshold). Otherwise, 'not_available'. + - `verifiedStatus`: true if the information provided was checked against another form of official identification, otherwise false. + - `identityMatchScore`: The overall score of identity information available in the Operator, information either provided in the request body comparing it to the one that the MNO holds or directly using internal MNO's information. It is optional for the Operator to return the Identity match score. + - `contentLock`: Indicates if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked). + - `parentalControl`: Indicates if the subscription associated with the phone number has any kind of parental control activated. + + ## Errors + + - If the authentication access token is not valid, a `401 UNAUTHENTICATED` error is returned + - If the API call contains a formatting or other any other syntactic error, a `400 INVALID_ARGUMENT` error is returned. + - If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API consumer has a valid access token that does not have the required scope to obtain Age Verification information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + - Other errors may be returned as specified below. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: 0.1.0 + x-camara-commonalities: 0.5 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +servers: + - url: "{apiRoot}/kyc-age-verification/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Age Verification + description: Operations to verify the age of a user. + +paths: + /verify: + post: + tags: + - Age Verification + summary: Verify Age Threshold + description: | + Verify that the age of the subscriber associated with a phone number is equal to or greater than the specified age threshold value. + + As it is possible that the person holding the contract and the end-user of the subscription may not be the same, the endpoint also admits a list of optional properties to be included in the request to improve the identification. The response may optionally include the `identityMatchScore` property with a value that indicates how certain it is that the information returned relates to the person that the API Client is requesting. To increase the reliability of the information returned, the API Provider may include in the response the `verifiedStatus` property, indicating whether the identity information in its possession has been verified against an identification document legally accepted as an age verification document. + + If the API Client indicates request properties `includeContentLock` or `includeParentalControl` with value `true` and the API Provider implements this functionality, then the response will also include `contentLock` and `parentalControl` properties to indicate if the subscription has any kind of content filtering enabled. On the other hand, if the request properties are not included or the API Client specifies value `false`, then the response properties will not be returned. If the API Provider doesn't implement this functionality, request properties will be ignored and response properties won't be returned in any case. + operationId: verifyAge + security: + - openId: + - kyc-age-verification:verify + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyRequestBody' + examples: + Two-Legged Access Token Example: + value: + ageThreshold: 18 + phoneNumber: '+34629255833' # Note: Only required in case a 2-legged flow has been agreed between API Provider and API Consumer; otherwise, do not include phoneNumber + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@example.com" + includeContentLock: true + includeParentalControl: true + Three-Legged Access Token Example: + value: + ageThreshold: 18 + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@gmail.com" + includeContentLock: true + includeParentalControl: true + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyResponseBody' + examples: + KYC_200Example: + value: + ageCheck: "true" + verifiedStatus: true + identityMatchScore: 90 + contentLock: "false" + parentalControl: "true" + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + VerifyRequestBody: + type: "object" + description: Request to verify the age threshold provided. + required: + - ageThreshold + properties: + ageThreshold: + $ref: "#/components/schemas/AgeThreshold" + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + idDocument: + $ref: "#/components/schemas/IdDocument" + name: + $ref: "#/components/schemas/Name" + givenName: + $ref: "#/components/schemas/GivenName" + familyName: + $ref: "#/components/schemas/FamilyName" + middleNames: + $ref: "#/components/schemas/MiddleNames" + familyNameAtBirth: + $ref: "#/components/schemas/FamilyNameAtBirth" + birthdate: + $ref: "#/components/schemas/Birthdate" + email: + $ref: "#/components/schemas/Email" + includeContentLock: + $ref: "#/components/schemas/IncludeContentLock" + includeParentalControl: + $ref: "#/components/schemas/IncludeParentalControl" + + AgeThreshold: + type: "integer" + minimum: 0 + maximum: 120 + description: The age to be verified. The indicated range is a global definition of maximum and minimum values allowed to be requested. It is important to note that this range might be more restrictive in some implementations due to local regulations of a country i.e. A country does not allow to request for an age under 18. This limitation must be informed during the onboarding process. + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + IdDocument: + type: "string" + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + Name: + type: "string" + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + GivenName: + type: "string" + description: First/given name or compound first/given name of the customer. + + FamilyName: + type: "string" + description: Last name, family name, or surname of the customer. + + MiddleNames: + type: "string" + description: Middle name/s of the customer. + + FamilyNameAtBirth: + type: "string" + description: Last/family/sur- name at birth of the customer. + + Birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + Email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + IncludeContentLock: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `contentLock` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + IncludeParentalControl: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `parentalControl` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + VerifyResponseBody: + type: "object" + description: Response to an age verification request + required: + - ageCheck + properties: + ageCheck: + $ref: "#/components/schemas/AgeCheck" + verifiedStatus: + $ref: "#/components/schemas/VerifiedStatus" + identityMatchScore: + $ref: "#/components/schemas/IdentityMatchScore" + contentLock: + $ref: "#/components/schemas/ContentLock" + parentalControl: + $ref: "#/components/schemas/ParentalControl" + + AgeCheck: + type: "string" + description: Indicate `"true"` when the age of the user is the same age or older than the age threshold (age >= age threshold), and `"false"` if not (age < age threshold). If the API Provider doesn't have enough information to perform the validation, a `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + VerifiedStatus: + type: "boolean" + description: Indicate `true` if the information provided has been compared against information based on an identification document legally accepted as an age verification document, otherwise indicate `false`. + + IdentityMatchScore: + type: "integer" + minimum: 0 + maximum: 100 + description: The overall score of identity information available in the API Provider, information either provided in the request body comparing it to the one that the API Provider holds or directly using internal API Provider's information. It is optional for the API Provider to return the Identity match score. + + ContentLock: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked) and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ParentalControl: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of parental control activated and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ErrorInfo: + type: "object" + required: + - status + - code + - message + properties: + status: + type: "integer" + description: HTTP response status code + code: + type: "string" + description: Code given to this error + message: + type: "string" + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token +``` diff --git a/marked/KnowYourCustomer/code/API_definitions/kyc-fill-in/raw.md b/marked/KnowYourCustomer/code/API_definitions/kyc-fill-in/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8cb797571ba3e5ea104b594d61bfc45fd298d564 --- /dev/null +++ b/marked/KnowYourCustomer/code/API_definitions/kyc-fill-in/raw.md @@ -0,0 +1,501 @@ +# kyc-fill-in + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Fill-in + + description: | + + This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + ## API Functionality + + This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + + * To fill-in the user personal data during the digital registration of an account to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + + * The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + + * For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + ### Special Scopes + + This API uses the following special scope kyc-fill-in:set-all which means that the API provider returns an API response as if all these scopes were specified in the scope value in the request: + `kyc-fill-in:phoneNumber kyc-fill-in:idDocument kyc-fill-in:name kyc-fill-in:givenName kyc-fill-in:familyName kyc-fill-in:nameKanaHankaku kyc-fill-in:nameKanaZenkaku kyc-fill-in:middleNames kyc-fill-in:familyNameAtBirth kyc-fill-in:address kyc-fill-in:streetName kyc-fill-in:streetNumber kyc-fill-in:postalCode kyc-fill-in:region kyc-fill-in:locality kyc-fill-in:country kyc-fill-in:houseNumberExtension kyc-fill-in:birthdate kyc-fill-in:email kyc-fill-in:gender` + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to request information related to an end user against the account data bound to their phone number. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + version: 0.3.0 + x-camara-commonalities: 0.5 + + +servers: + - url: '{apiRoot}/kyc-fill-in/v0.3' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Fill-in + description: Operations to provide information related to a customer identity stored the account data bound to the customer's phone number. + +paths: + /fill-in: + post: + tags: + - Fill-in + summary: Providing information related to a customer identity stored the account data bound to the customer's phone number. + + operationId: KYC_Fill-in + + security: + - openId: + - kyc-fill-in:set-all + - openId: + - kyc-fill-in:phoneNumber + - openId: + - kyc-fill-in:idDocument + - openId: + - kyc-fill-in:name + - openId: + - kyc-fill-in:givenName + - openId: + - kyc-fill-in:familyName + - openId: + - kyc-fill-in:nameKanaHankaku + - openId: + - kyc-fill-in:nameKanaZenkaku + - openId: + - kyc-fill-in:middleNames + - openId: + - kyc-fill-in:familyNameAtBirth + - openId: + - kyc-fill-in:address + - openId: + - kyc-fill-in:streetName + - openId: + - kyc-fill-in:streetNumber + - openId: + - kyc-fill-in:postalCode + - openId: + - kyc-fill-in:region + - openId: + - kyc-fill-in:locality + - openId: + - kyc-fill-in:country + - openId: + - kyc-fill-in:houseNumberExtension + - openId: + - kyc-fill-in:birthdate + - openId: + - kyc-fill-in:email + - openId: + - kyc-fill-in:gender + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_FillinRequest' + examples: + KYC_FillInBodyExample: + value: + { "phoneNumber": "+34629255833" } + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + + content: + application/json: + schema: + $ref: '#/components/schemas/KYC_FillinResponse' + examples: + KYC_Fillin200Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: 4 + postalCode: 1028460 + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: 36 + birthdate: '1978-08-22' + email: abc@example.com + gender: male + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + KYC_FillinRequest: + type: object + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + KYC_FillinResponse: + type: object + properties: + + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the id_document of the customer stored on the Operator's system. + + name: + type: string + description: Complete name of the customer stored on the Operator's system. It is usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer on the Operator's system. + + familyName: + type: string + description: Last name, family name, or surname of the customer stored on the Operator's system. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + middleNames: + type: string + description: Middle name/s of the customer stored on the Operator's system. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer stored on the Operator's system. + + address: + type: string + description: Complete address of the customer stored on the Operator's system. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address on the Operator's system. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address on the Operator's system. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: The postal code or Zip code of the customer's address, stored on the Operator's system. + + region: + type: string + description: Region/prefecture of the customer's address, stored on the Operator's system. + + locality: + type: string + description: Locality of the customer's address, stored on the Operator's system. + + country: + type: string + description: Country of the customer's address stored on the Operator's system. Format ISO 3166-1 alpha-2. + + houseNumberExtension: + type: string + description: House number extension of the customer stored on the Operator's system. Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: Birthdate of the customer, in ISO 8601 calendar date format (YYYY-MM-DD), stored on the Operator's system. + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain), stored on the Operator's system. + + gender: + type: string + description: Gender of the customer stored on the Operator's system (male/female/other). + enum: + - MALE + - FEMALE + - OTHER + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token +``` diff --git a/marked/KnowYourCustomer/code/API_definitions/kyc-match/raw.md b/marked/KnowYourCustomer/code/API_definitions/kyc-match/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..116e943733a9bd6b1711dc84ef9d6f2dc0c64c20 --- /dev/null +++ b/marked/KnowYourCustomer/code/API_definitions/kyc-match/raw.md @@ -0,0 +1,646 @@ +# kyc-match + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Match + + description: | + + This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + * **Match Score**: a numerical value that quantifies the similarity between two pieces of text based on the words they contain. This score is often used in various applications like text comparison, plagiarism detection, information retrieval, and natural language processing. The score typically reflects how well the words in one text match the words in another text. In the context of this API, this score will be used to determine how much does the input information looks like the information stored in the Operator's system. Unless otherwise captured in the implementation notes which Operators may publish, score will use the Jaro-Winkler distance algorithm for all countries. This parameter, as optional, will be returned depending on the capability of the Operator to calculate the scoring value. This means that not all Operators will implement this functionality or won't have the requested parameter available. It can happen that an Operator implements the score functionality but, for whatever reason, is not able to calculate it based on the client's input or the related stored information. For these cases, the score property related won't be returned in the response. + The range of score values is between "0" and "100", where higher scores indicate a higher similarity between the two compared parameters. + + ## API Functionality + + This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + + * To verify the user personal data during the digital registration of an account to a 3rd party service. + + * To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + + The API supports a multi-level hierarchy of property validation. In addition to the initial verification of the `phoneNumber`, an additional `idDocument` validation may occur based on different Operator requirements. This means that, in those cases, if the value of `idDocument` is not provided or it does not match the one bound to the specific phone number in the Operator systems, the operation will return an error. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the account data bound to their phone number. + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.3.0 + + x-camara-commonalities: 0.5 + +servers: + - url: '{apiRoot}/kyc-match/v0.3' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Match + description: Operations to match a customer identity against the account data bound to their phone number. + +paths: + /match: + post: + tags: + - Match + summary: Matching a customer identity by checking a set of attributes related against the account data bound to their phone number. + description: |- + Verify matching of a number of attributes related to a customer identity against the verified data bound to their phone number in the Operator systems. Regardless of whether the `phoneNumber` is explicitly stated in the request body, at least one of the other fields must be provided, otherwise a `HTTP 400 - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION` error will be returned. + + In order to proceed with the match check, some Operators may have the requirement to perform an additional level of validation based on the `idDocument` property. This means that, in those cases, the `idDocument` is required and the provided value needs to match the one stored in the Operator system associated with the indicated `phoneNumber`. This validation will be done before proceeding with the match check of the rest of the properties. The following two rules apply only in the cases where the Operator have the requirement to validate the `idDocument`: + - If no `idDocument` is provided, then a `HTTP 403 - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED` error will be returned. + - If the provided `idDocument` does not match the one stored in the Operator systems, then a `HTTP 403 - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH` error will be returned. + + The API will return the result of the matching process for each requested attribute. This means that the response will **only** contain the attributes for which validation has been requested. Possible values are: + - **true**: the attribute provided matches with the one in the Operator systems. + - **false**: the attribute provided does not match with the one in the Operator systems. + - **not_available**: the attribute is not available to validate. + operationId: KYC_Match + + security: + - openId: + - kyc-match:match + + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchRequestBody' + examples: + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + Three-Legged Without Phone Number Example: + value: + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchResponse' + examples: + KYC_Match200Example: + value: + idDocumentMatch: 'true' + nameMatch: 'true' + givenNameMatch: 'not_available' + familyNameMatch: 'not_available' + nameKanaHankakuMatch: 'true' + nameKanaZenkakuMatch: 'false' + middleNamesMatch: 'true' + familyNameAtBirthMatch: 'false' + familyNameAtBirthMatchScore: 90 + addressMatch: 'true' + streetNameMatch: 'true' + streetNumberMatch: 'true' + postalCodeMatch: 'true' + regionMatch: 'true' + localityMatch: 'not_available' + countryMatch: 'true' + houseNumberExtensionMatch: 'not_available' + birthdateMatch: 'false' + emailMatch: 'false' + emailMatchScore: 87 + genderMatch: 'false' + + '400': + $ref: '#/components/responses/Generic400' + + '401': + $ref: '#/components/responses/Generic401' + + '403': + $ref: '#/components/responses/Generic403' + + '404': + $ref: '#/components/responses/Generic404' + + '422': + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + KYC_MatchRequestBody: + type: object + description: Payload to validate the customer data. + + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + name: + type: string + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer. + + familyName: + type: string + description: Last name, family name, or surname of the customer. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan. + + middleNames: + type: string + description: Middle name/s of the customer. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer. + + address: + type: string + description: Complete address of the customer. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: Zip code or postal code + + region: + type: string + description: Region/prefecture of the customer's address + + locality: + type: string + description: Locality of the customer's address + + country: + type: string + description: Country of the customer's address. Format ISO 3166-1 alpha-2 + + houseNumberExtension: + type: string + description: Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + gender: + type: string + description: Gender of the customer (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + MatchResult: + type: string + enum: + - 'true' + - 'false' + - 'not_available' + + MatchScoreResult: + type: integer + description: Indicates the similarity score assigned to the input value when it does not exactly match the value stored in the operator's system. This property shall only be returned when the value of the corresponding match field is `false`. + minimum: 0 + maximum: 100 + + KYC_MatchResponse: + type: object + properties: + idDocumentMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether Id number associated to the ID document of the customer matches with the one on the Operator's system. + nameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the complete name of the customer matches with the one on the Operator's system. + nameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + givenNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether First name/given name of the customer matches with the one on the Operator's system. + givenNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether last name/ family name/ surname of the customer matches with the one on the Operator's system. + familyNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaHankakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Hankaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaHankakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaZenkakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Zenkaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaZenkakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + middleNamesMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the middle names of the customer matches with the one on the Operator's system. + middleNamesMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameAtBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the Family Name At Birth of the customer matches with the one on the Operator's system. + familyNameAtBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + addressMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete address of the customer matches with the one on the Operator's system. + addressMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street name of the customer matches with the one on the Operator's system. + streetNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNumberMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street number of the customer matches with the one on the Operator's system. + streetNumberMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + postalCodeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the postal code / zip code of the customer matches with the one on the Operator's system. + regionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the region of the customer's address matches with the one on the Operator's system. + regionMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + localityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the locality of the customer's address matches with the one on the Operator's system. + localityMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country of the customer's address matches with the one on the Operator's system. + houseNumberExtensionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the house number extension of the customer's address with the one on the Operator's system. + birthdateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the birthdate of the customer matches with the one on the Operator's system. + emailMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the email address of the customer matches with the one on the Operator's system. + emailMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + genderMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the gender of the customer matches with the one on the Operator's system. + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION: + description: Indicated param combination is invalid + value: + status: 400 + code: KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + message: Indicated parameter combination is invalid + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED + - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED: + description: The idDocument is required by the implementation + value: + status: 403 + code: KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED + message: The idDocument is required to perform the properties validation + KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH: + description: idDocument mismatch + value: + status: 403 + code: KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH + message: The idDocument needs to match the one associated with the provided phoneNumber + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided +``` diff --git a/marked/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..57b06aef04ea15329d39ec08c28a94325c03a451 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in/raw.md @@ -0,0 +1,40 @@ +# CAMARA KnowYourCustomer KYC Fill-in API + +(NOTE: This API description is supposed to be incorporated into the YAML definition file in the future releases.) + +This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + +## Relevant Definitions and concepts + +* **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + +## API Functionality + +This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + +* To fill-in the user personal data during the digital registration of an account to a 3rd party service. + +The following figure is the generic high-level flows of this API. + +KYC_Fill-in_flow + +Note: + +* Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + +* When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + +* The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + +* For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + +## Resources and Operations overview + +The API provides the following endpoint: + +* An endpoint to request information related to an end user against the acount data bound to their phone number. + + diff --git a/marked/KnowYourCustomer/documentation/API_documentation/KYC-Match/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/KYC-Match/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cbca168c95faec3b5331be7bf446e75eb8483c45 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/KYC-Match/raw.md @@ -0,0 +1,35 @@ +# CAMARA KnowYourCustomer KYC Match API + +(NOTE: This API description is supposed to be incorporated into the YAML definition file in a future release.) + +This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + +## Relevant Definitions and concepts + +* **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + +## API Functionality + +This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + +* To verify the user personal data during the digital registration of an account to a 3rd party service. + +* To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + +The following figure is the generic high-level flows of this API. + +KYC_Match_flow + +Note: + +* Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + +* When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + +## Resources and Operations overview + +The API provides the following endpoint: + +* An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the acount data bound to their phone number. + + diff --git a/marked/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f837f2947c4437abaf6904c2a3a23ffc0a966ef5 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
        **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
        **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
        1. The Customer:User has provided mandatory information of their identity
        2. Application developer has onboarded to MNO API
        3. Application developer has API credentials
        4. Privacy legal base requirement has been solved (Customer privacy)
        | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
        **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
        | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
        • Not Found: The number provided is not managed by the MNO
        • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
        | + +

        + +**User Story: KYC Fill-In - Get identity information of customer** +
        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
        **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
        **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
        1. The Customer:User has provided mandatory information of their identity
        2. Application developer has onboarded to MNO API
        3. Application developer has API credentials
        4. Privacy legal base requirement has been solved (Customer privacy)
        | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
        **Ends when:** The MNO service returns the identity information stored in its customer database.
        | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
        • Not Found: The number provided is not managed by the MNO
        • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
        | + + diff --git a/marked/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bec15552823f59c90eda301eefc660a52d7f2e7f --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-age-verification 0.1.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-age-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-age-verification.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/marked/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a959ba92a413d2a68516a35b0c96ab3701c0e34f --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-fill-in 0.3.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-fill-in.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-fill-in.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6dd37d0f8fb3690cb10616cb8ab36fe2e1b01380 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-match 0.3.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-match.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-match.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aeee6eceed1418cbc3cab2f4dd7c98506b47032d --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31/raw.md @@ -0,0 +1,92 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-10-31 + +*Tuesday, October 31st, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Ludovic Robert, Orange +* Efthymios Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Surajj Jaggernath, Vodacom + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introduction +* Proposed timeline and how to proceed +* Proposed Meeting Schedule +* Initial Codeowners +* Scope Proposal +* User Story – initial proposal +* AOB + +The Agenda was approved. + +## Introduction + +* As it was the first meeting, attendees introduced themselves to know each other. + +## Proposed timeline and how to proceed + +* Toshi showed Milestone Reference, which was GSMA (Open Gateway Product Workstream) created based on CAMARA subproject activity, with proposed timeline of each milestone including Milestone 10 stable YAML publication targeted on December 8th. +* The proposed timeline was agreed after the following clarification: + * Stable YAML publication is for both of KYC-Match and KYC-Fill-in with version 0.1 (or 0.x if applicable, but not 1.0). + * Dates of Milestone 4 & 5 was wrong and to be corrected (Oct -> Nov) [AP01], though their Week Numbers were correct. +* Toshi proposed to proceed with KYC-Match and KYC-Fill-in work in alignment with GSMA Milestone Reference, i.e. Scope & User Story -> Flow & Parameters -> YAML & Documents, as much as possible, and it was agreed. + +### Proposed Meeting Schedule + +* Toshi proposed regular meeting schedule and after discussion, it was agreed that **Bi-weekly meetings are held on Tuesday, 0900-1000 CET**. +* Note: + * 0830-0930 CET was first agreed, and then in AOB, it was changed 0900-1000 CET by Stefano’s request + * Weekly or Bi-weekly was discussed, and Members agreed with Bi-weekly as most of other CAMARA subprojects do. It is because work/discussion is supposed to be progressed on GitHub Issue/PR mostly and meetings are used for resolving issues which require real-time verbal discussion. + * However, ad-hoc meetings may be held on Tuesdays between Bi-weekly regular meetings, if needed. Meeting time for ad-hoc meetings will be decided considering any conflict with other meetings especially DeviceLocation. + * December 26th and January 2nd are to be discussed +* Meeting link for the regular meetings will be distributed by ML, and information on the regular meetings will be incorporated into GitHub KnowYourCustomer page. [AI02] + +## Initial Codeowners + +* Toshi proposed Tet Chiba and Fernando in addition to Toshi (current codeowner). +* Ludovic requested to add Gilles Renoux, Orange. Toshi will ask Administrators to add three. [AI03] + +## Scope Proposal + +* Toshi proposed Scope as [PR #6 Update README.md with modified Scope](https://github.com/camaraproject/KnowYourCustomer/pull/6) +* Toshi showed the PR explaining Scope is part of the first milestone (Milestone 4). There were opinions below: + * Other subprojects’ Scope have just little or very high level. Maybe depends on User Story. (Ludovic) + * It is important to set high level scope considering global market. No need for user consent as high level scope, as Match is sometimes legitimate and country dependent. Email address is one of the important attributes. (Huub) + * Scope should be minimum, and details should be discussed and agree in User Story and attributes discussion. (Efthymios) + * Don’t think ‘limited to 4G and 5G’ is needed. (Javier) +* As conclusion, Toshi to modify the PR #6 with concrete attributes e.g. Mobile phone number removed and consent related text removed. [AI04] + +## User Story – initial proposal + +* Toshi explained User Story is part of the first milestone (MS4), and showed a pptx material briefly explaining use case and flow of KDDI’s KYC-Match and KYC-Fill-in services aiming at it being used for base of User Story work. +* Ludovic suggested to look at the User Story of CarrierBillingCheckOut subproject as it is very good, and then he accepted volunteering work to draft User Story of KnowYourCustomer (KYC-Match and KYC-Fill-in), which was thanked for by Toshi and other members. +* Ludovic told that Gilles, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, would upload a PR for User Story after becoming one of the codeowners. [AI05] + +## AOB + +* Next meeting: November 14th, 0900-1000 CET + + +## Action Items + +* **AI#01.01** Toshi to correct dates of Milestone 4 & 5 in the proposed timeline Excel sheet and distribute to the subproject. + +* **AI#01.02** Toshi to distribute Meeting link for the regular meetings via ML, and also to incorporate the information on the regular meetings into GitHub KnowYourCustomer page. + +* **AI#01.03** Toshi to ask Administrator to add Tet Chiba, Fernando and Gilles Renoux, Orange to KnowYourCustomer codeowners. + +* **AI#01.04** Toshi to modify the PR #6 with concrete attributes e.g. Mobile phone number removed and consent related text removed. + +* **AI#01.05** Gilles Renoux, Orange, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, to upload a PR for User Story draft after becoming one of the codeowners. + +* **AI#01.06** Toshi to share meeting materials shown during the meeting. + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1a32da8e3281309e8e0e1e23ee882dd2090795be --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14/raw.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-11-14 + +*Tuesday, November 14th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Scope Discussion +* User Story Discussion +* Next Steps +* AOB + +The Agenda was approved. + +## New Member + +* Daniel Dierich introduced himself, as it was his first time to attend the KnowYourCustomer meeting. + +## Review MoM & Actions + +* MOM 2023-10-31 draft was approved. PR #11 can be merged and closed. +* All the Action Items at the first meeting AI#01.01 ~ 06 were marked 'closed', though some would be confirmed in the later agenda. + + +### Review Issues & PRs + +* [Issue #7 Age Verification API](https://github.com/camaraproject/KnowYourCustomer/issues/7) + * Toshi explained that one of the GSMA’s new API proposals 'Age Verification' will be discussed in the CAMARA TSC on Thursday this week or later and that it will be approved and assigned to KnowYourCustomer subproject, and then asked members' views. + * There were various views. For example, some said that Age Verification should be included in KYC Match API as one of its attributes, and some said that Age Verification should be an independent API from KYC Match because their use cases are different and their regulation on personal information protection tend to be different. + * Members' consensus was that as Age Verification API is useful, we are happy to welcome Age Verification API work, and that it should be a separate API from KYC Match API. +* For other issues/PRs, description in the meeting document were reviewed and approved. + +## Scope Discussion + +* Scope was approved as PR #6. +* Stefano commented that he has commented/ will comment to PR #2 and depending on how his comments would be treated, he might want to modify the current scope text, but that the current scope text is fine with him now. + +## User Story Discussion + +* Gilles drafted User Stories for KYC Match and KYC Fill-in as [PR #13](https://github.com/camaraproject/KnowYourCustomer/pull/13) last week, and Toshi has made comments just before the meeting and Gilles has already reflected the comments to PR #13. However, as members requested for time to review it, the PR was kept open for further discussion. +* All members were requested to review the User Story drafts PR #13 in order to approve the User Story by or at the next meeting. [AI 01] + + +## User Story – initial proposal + +* Toshi explained User Story is part of the first milestone (MS4), and showed a pptx material briefly explaining use case and flow of KDDI’s KYC-Match and KYC-Fill-in services aiming at it being used for base of User Story work. +* Ludovic suggested to look at the User Story of CarrierBillingCheckOut subproject as it is very good, and then he accepted volunteering work to draft User Story of KnowYourCustomer (KYC-Match and KYC-Fill-in), which was thanked for by Toshi and other members. +* Ludovic told that Gilles, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, would upload a PR for User Story after becoming one of the codeowners. [AI05] + +## Next Steps +* Toshi's proposal to start discussion about Flows and Parameters (Milestone 5) on GitHub as well as to start discussion about YAML in parallel, as they are related in general and we need to accelerate our discussion, was accepted. +* Toshi is to create issues for Flow discussion and Parameter discussion. [AI 02] +* Members were informed that there have been three YAMLs uploaded as PRs; [PR #2](https://github.com/camaraproject/KnowYourCustomer/pull/2) Telefonica's KYC Match, [PR #15](https://github.com/camaraproject/KnowYourCustomer/pull/15) KDDI's KYC Match and [PR #16](https://github.com/camaraproject/KnowYourCustomer/pull/16) KDDI's KYC Fill-in. + +## AOB + +* Stefano proposed to add calculating match score feature to KYC Match API, as it is a very useful feature according to Hutchison's experience. +* Javier supported the idea of adding the feature, however, it will make our API work complex, so, it would be better to move the feature to the next version and keep the initial version simple. +* Tet seconded Javier’s comment, adding that KYC Match's first phase should be simple True/False response feature and Stefano's proposal should be tackled in the future versions. +* Members agreed that calculating match score feature would be discussed in the future versions. Toshi would consider how to note it, e.g. creating API's feature roadmap, creating an issue. [AI 03] +* Daniel asked the conclusion about Age Verification API at today's meeting. Toshi explained that it would depend on TSC meeting to be held on this Thursday and that it is likely that the API would come to KnowYourCustomer subproject. +* Huub asked if there was the agreed Attributes list and commented that KYC Attributes are different in each country, adding unique examples in the Netherlands. Toshi replied there is no agreed list yet and it should be discussed in the Parameters discussion. Gilles commented that User Story draft has some example attributes. Fernando commented that we should define compromised common properties. +* Next meeting: November 28th, 0900-1000 CET + +## Action Items + +* **AI#02.01** All members were requested to review the User Story drafts PR #13 in order to approve the User Story by or at the next meeting. + +* **AI#02.02** Toshi is to create issues for Flow discussion and Parameter discussion. + +* **AI#02.03** Toshi would consider how to note "calculating match score feature”, e.g. creating API’s feature roadmap, creating an issue. + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d724e57432ded57702e5b852d6dc5bbba1581f61 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28/raw.md @@ -0,0 +1,82 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-11-28 + +*Tuesday, November 28th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT +* Kazuma Kamiyama, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* User Story Discussion +* Parameters Discussion +* Next Steps including API Documentation +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MoM 2023-11-14 draft was approved. PR #17 can be merged and closed. +* Actions: + * AI #02.01 has been closed. + * AI #02.02 is to be closed today. + * AI #02.03 is kept open. + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show Issues and PRs status, which were noted. + +## User Story Discussion + +* Discussion on User Story PR #13 has been ongoing on GitHub. Discussion point is whether Match Score related phrases are included or not. Toshi proposed not to include them before the meeting to conclude the User Story, based on comments that the User Story should reflect the current scope of the API. +* During the meeting, Stefano commented that it would be better to include potential new functionality like Match Score in the User Story. However, Huub commented that we should be careful to include Match Score, because there are potential issues for Match Score, i.e., for example, there are many ways and solutions for Match Score and also some additional solution like Hashing should be introduced in terms of Privacy protection. +* As conclusion of the discussion, Match Score still needs to be discussed more in the future release, so, it was decided that Match Score related phrases will be incorporated into the User Story when it is discussed. Thus, the latest version of the User Story was agreed, and PR #13 can be merged and closed. + +## Parameters Discussion + +* To conclude our Parameter discussion, Toshi has created the list of our discussion points on the Parameter. +* On Bullet No.1 'How to handle some country/market specific attributes e.g. name reading, user information, idDocument', User information was discussed by using most of the remaining meeting time. +* There were several comments on User information as below (not exhaustive) : + * Same as KDDI, many operators have Subscriber (who has contract with operator) and User (who actually uses the mobile terminal). However, Huub commented that it is not understandable that there are just a few attributes for User, and that there should be the same attributes for User as for Subscriber. He further commented that it may be better to have two different APIs, i.e. one for Subscriber information match and one for User information match. + * Javier commented that customer needs are only for Subscriber information match, or there is no need to differentiate Subscriber and User and it is needed to simply match information like phone number, name, address etc. + * Toshi commented that KDDI is providing KYC-Match API with User information for Name, Name reading and Birthdate as commercial service, and that typically Subscriber is a parent and User is his/her child, and User’s other information is not provided (no customer needs), e.g. User's address is supposed to be the same as Subscriber’s. But there was a comment from Huub that this is not the case and that Even if User is a child of Subscriber, User (the child) may have a different address and other information separate from Subscriber's. +* Regarding Bullet No.1 for User information, KDDI was to consider how it could be handled and get back to the group. [AI #03.01] +* Regarding Bullet No.2, it was agreed to use the camelCase notation for parameter/attribute names, to follow the CAMARA API Design Guidelines . +* Due to time limitation, other discussion points could not be covered, so, Toshi will upload them on GitHub [AI #03.02] and all group members are requested to review and discuss them. [AI #03.03] + +## Next Steps + +* There was Toshi’s proposal to start discussion about API documentation, sharing proposed Skeleton based on QoD v0.8.0’s documentation. +* Toshi will upload it on GitHub as issue/PRs [AI #03.04] and all group members are requested to review and discuss them. [AI #03.05] + +## AOB + +* Next meeting will be December 12th (Tue) 0900-1000 CET. +* As we need more progress, we will have another meeting on December 19th (Tue) potentially. Time to be confirmed checking DeviceLocation regular meeting. + +## Action Items + +* **AI #03.01** Regarding the Parameter discussion, for User information, KDDI is to consider how it is handled and get back to the group. + +* **AI #03.02** Regarding the Parameter discussion, several discussion points could not be covered, so, Toshi will upload them on GitHub for discussion. + +* **AI #03.03** Further to AI #03.02 above, all group members are requested to review and discuss them. + +* **AI #03.04** To start working on API Documentation, Toshi will upload issue/PRs on GitHub related to it for discussion. + +* **AI #03.05** Further to AI #03.04 above, all group members are requested to review and discuss them. + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..456daf5b0e67c8add77815aab2c55ce382ab00c3 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12/raw.md @@ -0,0 +1,150 @@ +# CAMARA KnowYourCustomer meeting - MOM-2023-12-12 + +* Tuesday, December 12th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Revised timeline +* KYC Match +* KYC Fill-in +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MoM 2023-11-28 draft was approved. PR #20 can be merged and closed. +* Actions: + * Closed: AI#02.02, AI#03.01, AI#03.02, AI#03.03 + * Kept open: AI#02.03, AI#03.04 + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. + +## Revised Timeline + +* Revised timeline was shared on Page 7 in the agenda slides. The completion date of the initial version had been changed from December 8th to December 22nd. Toshi mentioned that he had spoken to GSMA and that they accepted the change. +* Target dates for some milestones are as below: + * Parameters agreed: ~December 12th (today) + * YAML completed: ~December 19th + * API documentation completed: ~December 19th + * Initial version published: ~December 22nd +* It was agreed that the next subproject meeting would be held on December 19th, 09-10 CET. +* Toshi asked team members whether the meeting time is ok, because the time is the same as Device Location meeting. The team members confirmed the meeting time is OK. Though one of two Telefonica regular members cannot attend, the other will cover. + +## KYC Match +## (1) Parameter discussion: Issue #18 + +* Are all the parameters optional? (DT) ->That is our understanding. (Toshi) +* Too many parameters. Should reduce the number. (TEF) +* It may be too many, but it should be ok as every parameter is optional. (KPN) +* Several parameters included in the list will be used in certain markets only. Naturally the list should include only parameters to be used commonly. (TEF) +* In terms of name, KPN thinks hashed initials are very useful so as to increase matching rate of First name and Family name. According to KPN's experience, that is effective not only for the Netherlands but also other markets. (KPN) +* Currently we are supposed to consider plain text only; not hashing. (TEF) +* To comply with GDPR, operators in the Netherlands always use hash, so parameters to be used for hash mode are required. (KPN) +* In Germany, operators always use hash. (DT) +* Same in UK. Same in Italy. It is better to think in European countries hash is always necessary. (Hutchison) +* Not necessary in Spain. The subproject has agreed that hash will be worked on in the future versions. (TEF) +* Not necessary in France. (Orange) +* There is no problem without hashing in Japan. (KDDI) +* Does anyone know Number Verification API's case, in terms of GDPR? (KDDI) ->Similar discussion is ongoing, I think. (KPN) +* As the team members know, the team members have agreed that additional features such as match scoring and hashing will be discussed in future versions. So **our first version is only for plain text mode. (Toshi) ->Agreed. (All)** +* It is fine, but in the Netherlands, plain text mode will not be used, so, some parameters that KPN has proposed to add for hash mode can be removed from the list for the initial plain text mode version. They are 'givenNameInitial' and 'middleNamesInitials'. (KPN) + + +* Is 'mainPhoneNumber' needed? As the group has agreed that Subscriber/User differentiation concept will be considered in the future versions, the current assumption should be that there is only one phone number. (TEF) +* Because KDDI's current implementation for providing commercial service uses 'mainPhoneNumber', KDDI would like to have it included, but as it seems to be unacceptable by the group, KDDI can compromise and agree to remove it from the list. (KDDI) + + +* There are two items 'cp_id' and 'service_id' included in the list. Don't understand they are needed. (Orange) +* As I have answered on GitHub, KDDI uses these two for 3rd party/API user identity, in addition to that included in the Access Token. They are not pure KYC parameters, but they are used for KDDI's implementation and existing service, so, KDDI would like to have them included in the list, if possible. (KDDI) +* Orange is not comfortable with them, as they are not KYC parameters. (Orange) +* It is true that they are not KYC parameters, but cp_id, which stands for 'content provider id', is used to identify 3rd party/API user, and service_id is used to identify a service brand for the 3rd party/API user's brands. (KDDI) +* If you want to use this kind of information, you can have it in the HTTP header and deal with it by API GW. It should not be in the list. (Hutchison) +* It is understood that opposing opinions against cp_id and service_id seem to be strong among the group members, as they are country/market specific and non-pure-KYC parameters. KDDI can compromise and agree to remove cp_id and service_id from the list. (KDDI) +**->Parameters for KYC Match API was agreed, as Issue #18 comment https://github.com/camaraproject/KnowYourCustomer/issues/18#issuecomment-1853339192.** + +## (2) KYC Match Request/Response parameter/attribute suffix discussion: Issue #22 + +* Final proposal: Request – no suffix, Response – add 'Match' (Orange proposal). +* Don't think it adds value. (TEF) +* OK to add Match to Response. Can differentiate Request and Response. (Hutchison) +* Useful. (KPN) +* As Orange, Hutchison, KPN and KDDI support "Request – no suffix, Response – add Match", I think the group can agree with it. (KDDI) +* Still don't think it adds value. (TEF) +* Better to look at Mobile Connect case. Suffix is not necessary, but adding suffix seems to work for application developers. (KPN) +* If all members other than TEF are happy with it, TEF can stop opposing. (TEF) +* Appreciated. (KDDI) + +**->Suffix to Parameters/attributes for KYC Match API was agreed, as below:** +| **attribute** | **Match Request** | **Match Response** | +| ------- | ----------------- | ------------------ | +|**attribute** | attribute | attributeMatch | +|**e.g. given name** | givenName | givenNameMatch | + +## (3) KYC Match API Error Response Codes discussion: Issue #24 + +* Final proposal is in Issue #24. Basically the response codes included in the TEF's initial YAML and those included in the KDDI's initial YAML are merged. +* Need some time to review the final proposal. (TEF) +* **All members are requested to review the response code final proposal (Issue #24) by COB Friday 15th Dec. [AI#04.01]** + +## (4) KYC Match API YAML definition: PR #27 + +* KDDI has proposed the consolidated YAML definition created as PR #27, which is based on TEF's YAML initial proposal, KDDI's YAML initial proposal and the group's past discussions. But currently no description added. (KDDI) +* **Toshi is to modify the consolidated YAML definition based on today's outcome for KYC Match API. [AI#04.02]** +* **All members are requested to review the consolidated KYC Match API YAML definition proposal (PR #27) by COB Friday 15th Dec. [AI#04.03]** +* Target date for KYC Match API YAML completion: 19th December (Tue) + +## KYC Fill-in + +* Regarding KYC Fill-in API, proposals on Parameters/Attributes, Parameter/Attribute suffix, Error Response Codes etc. have been input by KDDI in Issue #23, and there have been some discussions. (KDDI) +* **All members are requested to review the proposals in Issue #23 by COB Friday 15th Dec. [AI#04.04]** +* **Toshi to modify Parameters/Attributes proposal in Issue #23 based on today's KYC Match discussion outcome. [AI#04.05]** +* Same as KYC Match, KDDI has proposed the consolidated YAML definition created as PR #28, which is based on KDDI's YAML initial proposal and the group's past discussions. But currently no description added. (KDDI) +* **All members are requested to review the consolidated KYC Fill-in API YAML definition proposal (PR #27) by COB Friday 15th Dec. [AI#04.06]** +* Target date for KYC Fill-in API YAML completion: 19th December (Tue) + +## Next Steps + +* Target date for KYC Match and KYC Fill-in API documentation: 19th December (Tue) +* **Toshi to create Issue/PR for this. [remaining AI#03.04]** + +## AOB + +* **Next meeting: 2023/12/19(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #04.01** All - Review KYC Match API Error Response (Issue #24); due COB Friday 15th December + +* **AI #04.02** Toshi - Update KYC Match API Consolidated YAML definition proposal based on the outcome of the Tuesday's meeting + +* **AI #04.03** All - Review KYC Match API Consolidated YAML definition proposal (PR #27); due COB Friday 15th December + +* **AI #04.04** All - Review KYC Fill-in API specifications proposal (e.g. parameters/attributes) (Issue #23); due COB Friday 15th December + +* **AI #04.05** Toshi - Update KYC Fill-in API specifications proposal (e.g. parameters/attributes) based on the outcome of the Tuesday's meeting + +* **AI #04.06** All - Review KYC Fill-in API Consolidated YAML definition proposal (PR #28); due COB Friday 15th December + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..92c20283d071e0ed6986ffc9e696a59cb98e18e2 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19/raw.md @@ -0,0 +1,104 @@ +# CAMARA KnowYourCustomer meeting - MOM-2023-12-19 + +* Tuesday, December 19th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Timeline +* KYC Match (to complete the initial YAML and the API document) +* KYC Fill-in (to complete the initial YAML and the API document) +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2023-12-12 draft (PR #20) has been approved and merged. +* Actions: + * Closed: AI#02.03, AI#03.04, AI#04.01, AI#04.02, AI#04.03, AI#04.04, AI#04.05, AI#04.06 + * Kept open: None + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. + +## Timeline for the initial version + +* Reviewed the timeline: + * YAML completed: ~December 19th (TODAY) + * API documentation completed: ~December 19th (TODAY) + * Initial version published: ~December 22nd + +## KYC Match + +* Toshi asked members if there are any remaining issues to discuss at the meeting, after mentioning that he understands our discussions on GitHub since our last meeting have cleared all Issues/PRs. +* There was no comment, and it was confirmed that PR #27 (Match YAML) and PR #31 (Match API Document) could be approved and merged. + +## KYC Fill-in + +* There were two remaining issues. +* **Issue #1: in PR #28 (Fill-in YAML), there is a proposal to add “Phone Number” (or MSISDN) to the Fill-in request body.** + * Members understood by GitHub discussions that putting Phone Number into the request body is not necessary, because it can be retrieved from 3-Legged AuthN/AuthZ/ConsentCapturing processes of this API. On GitHub discussions, Orange explained that it is needed for 2-Legged AuthN/Authz. KDDI explained during the meeting that CAMARA/Open Gateway have decided that 3-Legged AuthN/AuthZ processes are required for APIs touch user privacy information including KYC Match/Fill-in APIs. + * If there is no Phone Number in the request body, it will degrade usability of the API. Also, it is better to have Phone Number when it comes to combination with other APIs. It is not understandable why KDDI thinks it is not needed? (DT) + * More than one phone number is used for IoT Devices and Family Member service case, so, it is better to add “Phone Number” to the request body to show which phone number is the target phone number for the KYC Fill-in request, which leads to better usability. (DT) + * The concept of more than one phone number was proposed by KDDI before, and after the group discussion, it was not adopted and left for future enhancement because it will make things complicated. So, if it is related to more than one phone number, it should be discussed in the future release. So, for our initial version, is it ok that Phone Number attribute is not included in the request body? (Toshi) + * Agreed. (DT, Orange, Telefonica) + +* **Issue #2: in PR #32 (Fill-in API Document), there is a question by Orange about KDDI proposed KYC Fill-in API operation/ service sequence; 3rd parties should make contract with MNO (KDDI) for the API use, when 3rd parties shou ld decide which information/ attributes they will receive by an API call, and the 3rd party ID, which a 3rd party is given by MNO when making contract, should only be included in the Fill-in API request body.** + * As 3rd party Id can be retrieved by AuthN/AuthZ/Consent Capturing processes (Client ID), there is no need to include 3rd party Id in the request body. (Orange) + * If the 3rd Party Id is not included in the request body, there would be no attribute parameter in the Fill-in API request body. Is it no problem? (Toshi) + * No problem. (Orange) + * KDDI’s Fill-in API operation/ service sequence forces 3rd parties to decide which information/ attributes they can receive by an API call. This is for better security / privacy protection. MNO can control which information/ attributes a 3rd party will receive, considering its scale, business areas, credit quality and so on. (KDDI) + * Because there is no information sent from a 3rd party to MNO in the request body, it is up to the MNO to decide which information/attributes the 3rd party will receive. Is this OK? Also, in terms of security and privacy protection, the MNO should be responsible for that. Is this OK, as well? (Toshi) + * OK. (Orange) + * I will write down these somewhere in the API document and/or the YAML description. (Toshi) + * As the 3rd party id can be retrieved by AuthN/AuthZ/Consent Capturing processes, it seems it is the same situation as the Phone Number. So, it should be discussed in the future releases. (DT) + * OK. (KDDI) + +## Next Steps + +* **KYC Match API:** as the YAML (PR #27) and the API Document (PR #31) are fixed, these two PRs are to be merged within today as it is. + * **Codeowners (Fernando, Gilles) to approve the PRs. [AI#05.01]** + * **Then Toshi to merge the PRs. [AI#05.02]** + +* **KYC Fill-in API:** the YAML (PR #28) and the API Document (PR #32) will be modified according to today’s outcome. Then the modified PRs will be merged within today. + * **Toshi to modify the YAML and the API document according to today’s outcome [AI#05.03]** + * **Then Codeowners (Fernando, Gilles) to approve the PRs. [AI#05.04]** + * **Then Toshi to merge the PRs. [AI#05.05]** + +* **Next steps after the Christmas Break:** + * Initial version agreed today (v0.1.0): Error correction, missing information, improvement of API description + * Next version (v0.2.0): leftover issues, new features, functional enhancement + * Age verification API to start + +## AOB + +* **Next meeting: 2024/1/9(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #05.01** For KYC Match API, Codeowners (Fernando, Gilles) to approve PR #27 and PR #31 +* **AI #05.02** Then Toshi to merge the PRs +* **AI #05.03** For KYC Fill-in API, Toshi to modify the YAML and the API document according to today’s outcome +* **AI #05.04** Then Codeowners (Fernando, Gilles) to approve the modified PRs. +* **AI #05.05** Then Toshi to merge the approved PRs. + + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..18c7b111fb7703c8ea21de0ee7e6ba8873c7d126 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09/raw.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-01-09 + +* Tuesday, January 9th, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2023-12-19 draft (PR #33) has been approved and merged. +* Actions: + * Closed: none + * Kept open: none + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. It was agreed that all the current issues and PRs were for v0.1.0 and could be closed. **->To close all the issues and PRs. (Toshi) [AI#06.01]** + +## Next Steps + +**(1) v0.1.0** +* Making the -rc version and the release version as well as making the release branch & Changelog.md is just a common process. Don’t think there is any error correction needed and any missing information. Concern is that parameter/attribute descriptions are enough or not. (Telefonica) + +* Agree. We may need to add parameter/attribute descriptions. Will create an issue/PR for this. (Toshi) **->To create an issue/PR for adding parameter/attribute descriptions (Toshi) [AI#06.02]** + +* Regarding "application/json;charset=utf-8 or application/json" and "#/components/headers/x-correlator", **Toshi will check Commonalities discussion in order to decide if there is anything to do for v0.1.0. (Toshi) [AI#06.03]** + +**(2) v0.2.0** + +* Toshi listed up leftover issues, new features, functional enhancement etc. which were identified during the v0.1.0 discussions. There was no comment to delete any items from the list, so, all items were regarded as v0.2.0 candidate items. **->Toshi to create issues for each item. (Toshi) [AI#06.04]** + +* Regarding the item (7), Mobile Connect-like Match response (Y, N-NA, N-AV, N-AD), **DT will discuss it internally with their experts about Error Reponses etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (DT) [AI#06.05]** + +* Regarding the item (9), Gender attribute, **Telefonica will discuss it internally with their experts about Privacy etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (Telefonica) [AI#06.06]** + +* Regarding the item (11), **Toshi will arrange for OIDF to make a presentation about their eKYC-IDA activity during the next KnowYourCustomer SP meeting (or a later meeting). (Toshi) [AI#06.07]** + +* Regarding the item (11), having been asked, DT replied that Dawid Wrobleswski takes part in the Identity and Consent Management WG, and that DT takes part in OIDF but it is not clear that DT is engaged actively in eKYC-IDA. (DT) + +**(3) Age Verification API** + +* Orange wants to start Age Verification discussion, but Gilles is not the person responsible for the topic. Toshi has asked GSMA to identify the responsible person and is waiting for their reply. + +## AOB + +* **Next meeting: 2024/1/23(Tue) 0900-1000 CET.** Hopefully OIDF’s eKYC-IDA presentation will be included. + +* DT asked to add 'Efthymis Isaakidis, DT' as attendee to MoM-20231212 and MoM-20231219. (DT) **->Toshi to create PRs. (Toshi) [AI#06.08]** + +## Action Items + +* **AI #06.01** It was agreed that all the current issues and PRs were for v0.1.0 and could be closed. ->To close all the issues and PRs. (Toshi) + +* **AI #06.02** For v0.1.0, to create an issue/PR for adding parameter/attribute descriptions (Toshi) + +* **AI #06.03** Regarding “application/json;charset=utf-8 or application/json” and “#/components/headers/x-correlator”, Toshi will check Commonalities discussion in order to decide if there is anything to do for v0.1.0. (Toshi) + +* **AI #06.04** For all the listed up items, Toshi to create issues for each item as v0.2.0 candidate items. (Toshi) + +* **AI #06.05** Regarding the item (7), Mobile Connect-like Match response (Y, N-NA, N-AV, N-AD), DT will discuss it internally with their experts about Error Reponses etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (DT) + +* **AI #06.06** Regarding the item (9), Gender attribute, Telefonica will discuss it internally with their experts about Privacy etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (Telefonica) + +* **AI #06.07** Regarding the item (11), Toshi will arrange for OIDF to make a presentation about their eKYC-IDA activity during the next KnowYourCustomer SP meeting (or a later meeting). (Toshi) + +* **AI #06.08** Toshi to create PRs for adding ‘Efthymis Isaakidis, DT’ as attendee to MoM-20231212 and MoM-20231219. (Toshi) diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..46ee5a48327c07e99fab32ce0d6f2163277e0d02 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23/raw.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-01-23 + +* Tuesday, January 23rd, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2024-01-09 draft (PR #41) had been approved by the codewoners, however, an error in writing was found in Action Items. It was corrected a few hours before the meeting and the codeowners were requested to approve it again. + +* Actions: + * Closed: AI #06.08 + * Kept open: AI #06.01, #06.02, #06.03, #06.04, #06.05, #06.06, #06.07 + +### Review Issues & PRs + +* [Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18) KYC Match - Compare specifications + * (for v0.1.0) Javier TEF and Huub KPN commented in Github. Once AI#06.02 has covered these comments, this issue will be closed. + +* [Issue #37](https://github.com/camaraproject/KnowYourCustomer/issues/37) Include API description in yaml + * (for v0.1.0) Ongoing. PR #44 and PR #45 have been created by Toshi KDDI. Once these two PRs have been merged, this Issue can be closed. + +* [Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38) Proposition of design evolution + * Ongoing discussion. + +* [Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39) Polymorphism and discriminator for specific requirement + * Ongoing discussion. PR #43 has also been created by Gilles Orange, but it is not-to-be-merged. Aim is to identify Market/Country specific attributes in yaml, by using Polymorphism and discriminator. Device Location uses similar methods. (Orange) + * This way may make the API more complicated. There may be other ways than something in yaml, e.g. routing solutions with aggregators. (HUT) + * How aggregators know the market/country could be an issue. (TEF) + * As the discussion was very good but it was difficult to catch the details, Toshi KDDI requested Stefano HUT to make comments in the GitHub. + +* [Issue #40](https://github.com/camaraproject/KnowYourCustomer/issues/40) CHANGELOG.MD + * (for v0.1.0) Ongoing. CHANGELOG.MD is needed for v0.1.0 release. To be reviewed and corresponding PR to be created. + +* [PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43) Match API Design evolution proposal + * PR related to issue #39. Ongoing. Please discuss in Issue #39. + +* [PR #44](https://github.com/camaraproject/KnowYourCustomer/pull/44) Update kyc-match.yaml to include API description in yaml + * (for v0.1.0) Related to issue #37. Quick merge is expected, as it is just to make API description kyc-match.md included in the yaml, but SP members are requested to review. [AI#07.01] + +* [PR #45](https://github.com/camaraproject/KnowYourCustomer/pull/45) Update kyc-fill-in.yaml to include API description in yaml + * (for v0.1.0) Related to issue #37. Quick merge is expected, as it is just to make API description kyc-fill-in.md included in the yaml, but SP members are requested to review. [AI#07.02] + +## AOB + +* Efthymis DT raised an issue as a v0.2.0 topic. + * In terms of connection with Channel Partner, customer information protection could be an issue. In principle, user's authorization mechanism exists, but malicious application developers or those who access illegally might cause leak of customer information. Data minimization should be considered, and it is necessary to introduce some mechanism, with which only limited information can be accessed by application developers or aggregators, based on their use cases shared with operators when onboarding. This is both for KYC Match and KYC Fill-in APIs. (DT Efthymis) + * One solution would be to decide which personal information a channel partner can be access between a channel partner and an operator. Another solution would be hashing to avoid transmitting KYC information as plain text. (HUT Stefano) + * Regarding hashing, DT's implementation uses hashing for part of Match and Fill-in as the necessary feature. (DT Efthymis) + * Toshi asked Efthymis to create an issue for a new discussion topic, and Efthymis agreed to do it. [AI#07.03] + * Toshi explained that KDDI's Fill-in service has a process that when a third party makes contract with KDDI for the Fill-in service, both decide what information the third party can get by calling Fill-in API. A third party puts its 3rd party ID in the Fill-in API request body, and on receiving the 3rd party ID, KDDI provides limited information based on the contract. This measure was proposed for Fill-in v0.1.0, but it was not accepted by the group. (KDDI Toshi) ->It could become a solution. (DT Efthymis) + * Another potential solution is to use "scope" to limit information that the Channel Partner can handle. (DT Efthymis) + * Using "scope" has been discussed in CAMARA Identity and Consent Management WG (ICM). It relates to CIBA Flow and Operate API for onboarding. But the ICM documentation is still in progress. It is recommended for KYC APIs to introduce the mechanism for privacy protection once the ICM documentation has been matured enough. (DT Rafal) + +* **Next meeting: 2024/2/6(Tue) 0900-1000 CET.** OIDF's eKYC-IDA presentation is planned. + +## Action Items + +* **AI #07.01** SP members are requested to review PR #44. (All SP members) + +* **AI #07.02** SP members are requested to review PR #45. (All SP members) + +* **AI #07.03** DT Efthymis is to create a Privacy Protection related issue for a new discussion topic. (DT Efthymis) + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..97395179d201cebdc647116d84a39e4b8c3b1e7d --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06/raw.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-02-06 + +* Tuesday, February 6th, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica +* (Guest) Mark Haine, OIDF +* (Guest) Kosuke Koiwai, OIDF/KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Guest presentation – OIDF eKYC-IDA +* Review Issues & PRs +* AOB + +The Agenda was approved. + +Javier Carro Telefonica commented that Telefonica would like to resolve open issues for v0.1.0 quickly and release v0.1.0 soon, due to requirement from their product team and business team. + +->Toshi agreed with early release of v0.1.0, and proposed to discuss it after OIDF presentation. + +## Guest presentation – OIDF eKYC-IDA + +* Mark Haine, OIDF eKYC-IDA WG chair, introduced their activity using his presentation materials. (The presentation materials have been shared with the subproject members after the meeting, by email circulation and by uploading to the repo.) +* It was mentioned that three products exist in UK and Germany etc. How is Consent Management dealt with? (Telefonica) +* ->In Germany, Yes.com provides Identity Assurance information to a large number of banks. Consent confirmation attribute is used in OIDC process. (Mark) +* How about others? (Toshi) +* ->Another case is Government Citizen identity system. OIDC plus sharing consent confirmation results. (Mark) +* ->Another case is ConnectID in Australia. Like Yes.com, it provides Identity Assurance information to banks. (Mark) +* ->Conformance tests were completed in these cases. (Mark) +* If CAMARA KYC-Match and KYC-Fill-in APIs adopt OIDC eKYC-IDA, what benefit it would receive? (Toshi) +* ->If the APIs are used for many use cases, interconnectivity will be improved, in terms of data structure. When new objects to share with application developers appear, it is easier to utilize Meta data etc. It would be possible to change range of data to share with each application developer, so it will lead to data minimization. (Mark) +* If there is a specific use case with CAMARA/Open Gateway, Mark can create and share example response messages. (Mark) +* Toshi asked Mark to continue information sharing and discussion, and Mark kindly agreed. +* Toshi will an Issue to discussion collaboration with OIDF eKYC-IDA. [AI#08.01] + +## Review MoM & Actions + +* MOM 2024-01-23 draft (PR #48) and Uploading the meeting material (PR #49) are approved and to be merged. + +* Actions: + * Closed: AI #06.01, #06.02, #06.07, #07.01, #07.02, #07.03 + * Kept open: AI #06.03, #06.04, #06.06 + +## Review Issues & PRs + +* Issue #18 KYC Match - Compare specifications (Issue #18) + * (for v0.1.0) To be closed soon, as discussion on description of parameters is closing. + +* Issue #37 Include API description in yaml (Issue #37) + * (for v0.1.0) To be closed, as PR #44 and PR #45 are to be merged. + * Apart from this Issue and related PRs, the remaining issue is the description of parameters, related to Issue #37. Toshi will create corresponding PRs, but as description of parameters in the current YAMLs are not needed to be modified much according to his reading, Toshi thinks the PRs could be simple and approved soon. + * Telefonica requested to complete the remaining issues and release v0.1.0 by end of this week. + * Toshi agreed and told he would create PRs today or tomorrow, and asked all to review the PRs so that they could be approved within this week. + +* Issue #46 and PR # 50 + * (for Age Verification) Gilles Orange pointed out that there has been no comments for Age Verification Issue/PR, and shared his concern that it may not be completed by end of March, which had been requested by GSMA. + * Call for action: all to review the Issue and PR for Age Verification and to be encouraged to discuss actively on GitHub. [AI#08.02] + +## AOB + +* **Next meeting: 2024/2/20(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #08.01** Toshi will an Issue to discussion collaboration with OIDF eKYC-IDA. (KDDI Toshi) + +* **AI #08.02** All to review the Issue and PR for Age Verification and to be encouraged to discuss actively on GitHub. (All) + + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9f65c3ec9c44494de465a16028d6a4bec42dfa61 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20/raw.md @@ -0,0 +1,100 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-02-20 + +* Tuesday, February 20th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-02-06 draft ([PR #56](https://github.com/camaraproject/KnowYourCustomer/pull/56)) is ready to merge. + +* Uploading the meeting material ([PR #54](https://github.com/camaraproject/KnowYourCustomer/pull/54)) has been merged and it has been uploaded. +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.04, #06.06, #08.01, #08.02 + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – working on error correction and other refinement to create a release version + +* Issue #37 Include API description in yaml ([Issue #37](https://github.com/camaraproject/KnowYourCustomer/issues/37)) +* PR #44 Update kyc-match.yaml to include API description in yaml ([PR #44](https://github.com/camaraproject/KnowYourCustomer/pull/44)) +* PR #45 Update kyc-Fill-in.yaml to include API description in yaml ([PR #45](https://github.com/camaraproject/KnowYourCustomer/pull/45)) + * PR #44 and PR #45 have been approved and merged. + * Thus, including API description into yaml files has been completed, and Issue #37 can be closed. + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) +* PR #51 KYC-Match-Parameter Description Refine ([PR #51](https://github.com/camaraproject/KnowYourCustomer/pull/51)) +* PR #52 KYC-Fill-in-Parameter Description Refine ([PR #52](https://github.com/camaraproject/KnowYourCustomer/pull/52)) + * PR #51 and PR #52 have been approved and merged. + * Thus, refining parameter description in KYC Match and KYC Fill-in yamls has been completed, and Issue #18 can be closed. + +* Toshi KDDI told that he had some difficulty in creating a PR for uploading CHANGELOG.md, but Rafal DT replied that there is not anything different from other file uploading PRs. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing + * Gills Orange has responded to Toshi KDDI's comment. KDDI is to send reply comments. + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. PR #43 has been created by Gilles Orange for Issue #39, but it is not-to-be-merged. + * Gills Orange has responded to Toshi KDDI's comment. KDDI is to send reply comments. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. + * Gills Orange has commented for this issue. KDDI is to discuss internally and comment. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * OIDF Age Verification presentation to be arranged at the next meeting (Marth 5th) + * Gilles Orange has proposed the user story of Age Verification. KDDI and all KYC-SP members are expected to review the proposal. **AI #09.01** + * Huub KPN asked where Age Verification is discussed. ->Toshi replied that it is we KYC-SP that is discussing Age Verification and that Issue #46 is the issue to be looked at. + * Toshi suggested that Liberty Global might have interest in Age Verification, because they nominated Age Verification API for GSMA Open Gateway Product Workstream Drop #3 candidates. + + +## AOB + +* **Next meeting: 2024/3/5(Tue) 0900-1000 CET.** + +* There will be two CAMARA in-person events to held with MWC Barcelona, i.e. CAMARA meet and greet on Day1 at the MWC venue and CAMARA Evening Gathering on Day2 at a nearby hotel. Toshi encouraged all to attend and see each other in Barcelona. + + +## Action Items + +* **AI #09.01** Gilles Orange has proposed the user story of Age Verification. KDDI and all KYC-SP members are expected to review the proposal. (all) + +* **All other remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..75a73a56e938c515663849b064088cb53904d8d2 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05/raw.md @@ -0,0 +1,106 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-03-05 + +* Tuesday, March 05th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica +* Kiyoto Shinomura, KDDI +* Kosuke Koiwai, KDDI/OIDF +* Aziz Abouchi, SFR + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +Note: Presentation on Age Verification by OIDF has been postponed to our next meeting (19th March) or before, due to their unreadiness. + +Note: CAMARA had two events successfully during MWC24. 'Meet and greet' on Monday 26th at a meeting room in Fira Gran Via where MWC24 was held, and 'evening gathering' on Tuesday 27th at a hotel nearby. Hope to meet KYC SP members on another occasion. + + +## Review MoM & Actions + +* MOM 2024-02-20 draft as well as a corresponding PR was not yet created. (Toshi was sorry for that.) + +* Uploading the meeting material ([PR #58](https://github.com/camaraproject/KnowYourCustomer/pull/58)) was created a couple of hours before the meeting, so, review by SP members and approval by the code owners were expected. + +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.04, #06.06, #08.01, #08.02, #09.01(this was added after the Marth 05th meeting) + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – working on error correction and other refinement to create a release version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * It was supposed to be closed together with PR #51 and PR #52, but some discussions were ongoing. ->Need to check if the discussions can be moved to a new issue for v0.2.0. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It was supposed to be closed, but Stefano Hutchison has commented pointing out a new point. ->Need to check if the discussions can be moved to a new issue for v0.2.0., with Stefano who was absent from the meeting. + +* Issue #40 CHANGELOG.MD ([Issue #40](https://github.com/camaraproject/KnowYourCustomer/issues/40)) +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * After Rafal DT's comment at the last meeting on Feb 20th, Toshi successfully created a PR to upload CHANGELOG.MD as a new file, based on the Gilles' draft and modified for inclusion of API description into the yaml. Ready to be approved. + +* A new issue: Country/countryCode/countryName attribute and for countryCode alpha-2 or alpha-3 + * Issue to be created. **AI #10.01 (Toshi)** + +* Telefonica Javier Carro and Fernando proposed to remove 'phoneNumberMatch' attribute from KYC Match yaml, because, if the phoneNumber sent in the Match request is wrong, the process should be terminated by responding Error 403, so phoneNumberMatch becomes always 'true', so there is no need of it. + * Toshi asked Javier Carro and Fernando to create an Issue for that, so that it can be discussed by the SP. Specifically, Toshi told that KDDI needed to discuss internally and would send feedback to the issue. + * ->Telefonica also proposed to resolve this issue quickly by end of the week, so that KYC SP could publish the release version of Match/Fill-in v0.1.0, and then Fernando created the Issue #59 straightaway, and so, all members were requested to review the Issue as quickly as possible. **AI #10.02 (All)** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. PR #43 has been created by Gilles Orange for Issue #39, but it is not-to-be-merged. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * OIDF Age Verification presentation to be arranged at the next meeting (Marth 19th) or before. + + +## AOB + +* **Next meeting: 2024/3/19(Tue) 0900-1000 CET.** + + +## Action Items + +* **AI#10.01**: A new issue to be discussed - Country/countryCode/countryName attribute and for countryCode alpha-2 or alpha-3; Issue to be created. (Toshi) + +* **AI#10.02**: Issue #59 for Telefonica's proposal to remove 'phoneNumberMatch' attribute from KYC Match yaml; KDDI and all KYC-SP members are asked to review the proposal and send feedback as soon as possible; by Friday 8th at the latest. (all) +* **All other remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7016f14429555e0233ba20a5575aab7ef81c1a2a --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19/raw.md @@ -0,0 +1,130 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-03-19 + +* Tuesday, March 19th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kosuke Koiwai, KDDI/OIDF +* Aziz Abouchi, SFR +* (guest) Mark Haine, OIDF +* (guest) Dima Postnikov, OIDF + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* OIDF presentation re: Age Verification +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## OIDF presentation re: Age Verification + +* Presenters: + * Mark Haine, OIDF + * Dima Postnikov, OIDF +* Mark presented OIDC Advanced Syntax for Claims (ASC) including its concepts and its specification aspects. + * Outline of his presentation is captured at the bottom of this MoM. + * His slide deck has been shared by KYC-SP ML and uploaded to KYC-SP Repo. + * URL link to the current Advanced Syntax for Claims Work Group Draft: https://openid.bitbucket.io/ekyc/openid-connect-advanced-syntax-for-claims.html +* Dima shared how ConnectID AU introduced OIDC+IDA + ASC as a usecase in Australia. + * Outline of his presentation is captured at the bottom of this MoM. + * URL link to ConnectID AU spec: https://cdn.connectid.com.au/specifications/digitalid-identity-assurance-profile-05.html +* All thanked Mark and Dima for their presentation. +* All were requested to provide any feedback on the presentation. **AI #11.01** + + +## Review MoM & Actions + +* Due to lack of time, it was requested to review the related PRs and the actions list. +* MOM 2024-03-05 draft -> [PR #64](https://github.com/camaraproject/KnowYourCustomer/pull/64) +* Uploading the meeting 2024-03-05 material -> [PR #62](https://github.com/camaraproject/KnowYourCustomer/pull/62) +* Actions: + * Closed: AI #06.04, #10.01, #10.02 + * Kept open: AI #06.03, #06.06, #08.01, #08.02, #09.01 + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Due to lack of time, it was requested to review the related PRs and the actions list. + +### Match/Fill-in v0.2.0 – wip + +* Due to lack of time, it was requested to review the related PRs and the actions list. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * Toshi KDDI - As Age Verification API is a GSMA Open Gateway Drop #4 API, we should complete Age Verification v0.1.0 quickly. As Gilles has already created a proposal of the user story on GitHub, it is better for us to agree on the user story first. + * Toshi KDDI - In the Issue #46 discussion on GitHub, I found a problem was shared which I would agree with. The problem is that we verify the age against the contractor / subscriber data, not against the user who is currently using the handset. + * Gilles Orange - The proposal was that, for the initial version, the condition should be the owner of the contract is the user. If not, we cannot verify the age. (Gilles Orange) + * Toshi KDDI - replied that it made sense, adding a note that, during GSMA product portfolio work stream meeting on the day before, someone from Vodafone showed their interest in Age Verification API and asked GSMA for of Orange’s Age Verification API contact. + * Gilles Orange – His colleague may be contacted as they do not know the latest status. They thought we did not make any progress as they did not see anything in the main branch. + * Toshi KDDI – Vodafone also mentioned that they are interested in KYC Match API and together with Hatchison, they are going to do some input of some logic. Stefano may be aware of it. In the GSMA meeting, Toshi replied that any input would be welcome. + +## AOB +* From next meeting, Europe will be in summer time, but some countries including Japan do not have summer time, so we need to agree on our meeting time. As KDDI does not have problem with keeping the same meeting time for Europe and other countries having summer time, it was agreed that our meetings will be held for 0900-1000 CEST. +* **Next meeting: 2024/4/2(Tue) 0900-1000 CEST.** + + +## Action Items +* **AI#11.01**: All were requested to provide any feedback on the OIDF Age Verification presentation. (All) +* **All other remaining AIs** + + +## Appendix + +### Outline of Mark Haine’s presentation on OIDC Advanced Syntax Claims (ASC) +* (Page 1) This presentation was what Daniel Fett presented at OSW last year and adjusted. (OSW: OAuth Security Workshop) +* (Page 2) OIDC advanced syntax for claims was inspired by age verification use case so why he wanted to share this. +* But more than that, extend the use case, much more about requesting and receiving claims. Fine grained control over date delivery. RPs more control over what they get, a number of business reasons. +* Complex data structures, especially from IDA. Need better control of Json hierky claims., OIDC Core 2 levels vs IDA 5+ revels, difficult to control with OIDC mechanism. +* (Page 3) So ASC is no requirement for IDA, on top of any OIDC implementation. +Couple of special allowances for better use of. +* 2 important components, Transformed claims, age verification and others. Selective Abort/Omit. +* (page 4) Transformed Claims. +* (page 5) Usecase identified for Age Verification. Any convention, any version of age verification, over 16 or 18 or 21, varies in some countries. Retirement ages complex. +* Also ended up with transformed claims based on suffix on email, zip code, nationality (if contain multiple nationalities) etc. Allows us to return things derived from the base claims. +* (page 6) Idea: Claims values can be transformed using a small set of functions before any further evaluation is performed. +* (page 7) Example: Age Verification. Definition is above_18, then use – prefix ':' +* (page 8) In the draft spec, there are set of functions can be used, we think this is a decent set. Years_ago is application specific, but other than that is generalized. +* (page 10) We have spent a bit of time for simplification of implementation, IDP can add metadata to say only a subset is supported. Only allowing useful for age verification use case, also allow provide predefined transformed claims. Predefined claims to get above_18, simpler to execute for both parties. +* Also allow OPs to only support PTC. +* (page 11) Another example with PTC, Double colon indicates PTC, we do not need to define what above_18 means in the claims parameter +* (page 12) Another things discussed was UX consideration, show something meaningful to users to get consent is difficult. Worst case scenario say birth date (base claim) is provided. +* (page 14~17) Second feature, slightly more experimental slides. OIDC code feature essential:true, not widely implemented or understood. SAO, enable further data minimization. Allow for elements of the response to be conditionally left out. +We had a bit of troubles, Takahiko Kawasaki discovered a race condition, not deterministic. +* (page 18) What we came up is more flexible way of expressing the SAO feature without the race condition, Use JSON schema based definition +* (page 19) Example, for a verified_claims/claims, if it matches birthdate = 1900-01-01, omit all verified_claims/claims +* Effectively allows us condition, if a particular post code condition, if a post code is not London, omit address, or additional action, abort. Age verification. TSC, over the age of 13, abort the request if the user is under the age of 13. Minimum age of social media. We don’t want to ask users age, but don’t want to receive anything if the use is below 13. +* Come up with more general use such as post code, address, or with IDA, we only want to rely on verified identity if passport has been used or IAL2 and passport. Highly flexible, write conditions. +* Keep complexity under control, discuss taking it quite. Bit further, but decided not to go that far. Looked at some conditional languages, complexity and additional risks, large set of use cases, this set of feature will enable. We decided to not go too far to be a programming language. Relatively simple compared to other ways. +* More feedback will be valuable, trying to move to 1st ID. + +### Outline of Dima Postnikov’s presentation on ConnectID AU +* In AU, building national id infrastructure, ID scheme based on OIDC + IDA to start with, other methods Verifiable presentation. +* Advanced claims specs. In ConnecID Au, we use multiple specs. Not just OIDC+IDA, we ended up mixing multiple. +* Standard OIDC claims, verified_claims, +* Standard - typical name, phone, address etc., Advanced claims, 2 reasons, in future want to provide a lot of metadata. Additional metadata, how was the data verified, how long ago by whom, some non standard claims that OIDC not provide. Clear language over16,18,21,25,65, 18 is mainly used 95%, and bank account details. Lottery payout or insurance claims, telecom mobile number ownership. In future ASC, we will give me everything or nothing. RP don’t want to pay data unless full set. +* In AU, user OIDC + IDA, in future ASC. + +[END] + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9c134815b7118e29374aa151196b2410b7e9fc3c --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02/raw.md @@ -0,0 +1,102 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-04-02 + +* Tuesday, April 2nd, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Axel Nennker, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-03-19 draft -> [PR #68](https://github.com/camaraproject/KnowYourCustomer/pull/68), created on March 29th and asked to be reviewed ->No comments and approved +* Uploading the meeting 2024-03-19 material -> [PR #67](https://github.com/camaraproject/KnowYourCustomer/pull/67), has been approved and merged. +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.06, #08.01, #08.02, #09.01, #11.01 + * AI #08.02 and AI #09.01 are kept open, as both are for asking Team members to review Age Verification Issues and PRs. + * AI #11.01 is kept open, waiting for Team members’ feedback for OIDF Age Verification presentation. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. ->Need to check. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
        PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * We are continuing the exchange of opinions on Assurance levels and related matters on GitHub. (Orange Gilles) + * We should check the global situation. In Europe (eIDAS), three levels are defined. (KPN Huub) + * Also, the logic of the matching process needs further in-depth consideration and discussion. (KPN Huub) + * Next week, we will share relevant information. Depending on the subject, there are cases where plain text or hashes are used. (Hutchison Stefano) + * I am participating in a fuzzy logic conference/meeting. (Hutchison Stefano) + * The fuzzy logic discussion pertains to Age Verification as well as KYC Match. (Hutchison Stefano) + * Useful discussion. Please add the comments you made, to Issue #46. (Toshi KDDI) + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. Can user Story be approved? + * How the discussion on Issue #46 is going may require modifications of the draft User Story? (Toshi KDDI) ->Yes, likely. (Orange Gilles) ->So, the draft User Story cannot be approved now. Comments on typos have been input, anyway. (Toshi KDDI) + +* README.md should have Age Verification + * The top page of KYC-SP's GitHub Repo should have Age Verification-related text as part of Scope. (Toshi KDDI) -> Toshi is to draft text. **AI #12.01 (Toshi)** + + +## AOB +* **Next meeting: 2024/4/16(Tue) 0900-1000 CEST.** +* Linux Foundation requested all Camara API subprojects and Working Groups to move their regular calls to Zoom platform. KYC-SP meetings will move to Zoom platform once we are ready for that. + + +## Action Items +* **AI#12.01**: The top page of KYC-SP's GitHub Repo should have Age Verification-related text as part of Scope. Toshi is to draft text. [Toshi] +* **All other remaining AIs** + +[END] + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..82c1e5052c82af6096e347a81f01225561883cd7 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16/raw.md @@ -0,0 +1,118 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-04-16 + +* Tuesday, April 16th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Surajj Jaggernath, Vodacom +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-04-02 draft -> [PR #72](https://github.com/camaraproject/KnowYourCustomer/pull/72), created on April 12th. ->No comments and approved. +* Uploading the meeting 2024-03-19 material -> [PR #73](https://github.com/camaraproject/KnowYourCustomer/pull/73), has been approved and merged. +* Actions: + * Closed: AI #06.03 + * Kept open: AI #06.06, #08.01, #08.02, #09.01, #11.01, #12.01 + * AI #06.03 was closed, as per Telefonica Fernando's comment that Commonalities WG has concluded on "application/json;charset=utf-8 or application/json" and "#/components/headers/x-correlator" so AI #06.03 can be closed. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. Toshi is to take care of it. **AI #13.01 (Toshi)** + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. Toshi is to take care of it. **AI #13.02 (Toshi)** + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. ->Need to check after the meeting. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
        PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->Continue discussion on GitHub + * Huub KPN commented that the Issue includes many items in the list, and that it is better to split the items into each Issue, so that we can decide each item to be discussed, to be closed, or to be delayed. -> Toshi is to create Issues for each item. **AI #13.03 (Toshi)** + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * A new issue for Correction. + * I would change streetNumber to houseNumber. This is not an issue in the Netherlands, but in some countries, e.g. US, they have 1st East St., 2nd East St. 3rd East St. etc., Street Name has numbering, and it may confuse the streetNumber attribute. Proposal is to have streetName, houseNumber, houseNumberExtension.) (Huub KPN) + * In Spain, in residential areas, streetName and streetNumber may be enough, but in the city, streetName and streetNumber can identify the building, where many houses with each houseNumber exist, so streetNumber and houseNumber is different. (Fernando TEF) + * In that case, houseNumberExtension can be used to differentiate in the Netherlands. (Huub KPN) + * In US, streetName has numbering, so, streetNumber attributes may confuse people thinking it is street numbering or houseNumber, they say. (Huub KPN) + * In Spain, streetName is unique, and numbering is not used. (Fernando TEF) + * In France, same. (Gilles Orange) + * If we change streetNumber to houseNumber to solve US’s problem, it may cause other problem with other countries having different systems. (Fernando TEF) + * How about other standardization like Mobile Connect? (Huub KPN) + * Will check TM Forum. (Gilles Orange) + * Will check OIDF. (Toshi KDDI) + * Let’s compare other standardization cases and continue discussion on GitHub. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * It seems to converge into Jaro Winkler as the preferred method for doing fuzzy name logic. That is one conclusion that we can have already. (Huub KPN) + * Yes. (Gilles Orange) + * KDDI is still discussing this internally, and especially is concerned that fuzzy name logic is not needed for Japanese language. (Toshi KDDI) + * It is understood that Japan does not need fuzzy name logic and would use exact match. It can use 100% always for Jaro Winkler. But, in EU market, fuzzy name logic is required. (Huub KPN) + * Understood. From KDDI point of view, it would be better to make fuzzy name logic an optional feature and make Age Verification API workable without it. (Toshi KDDI) + * Understood. In EU markets, Normalisation is also required. Remove specific language characters and some funny characters. Mobile Connect does this. (Huub KPN) + * Do you mean that fuzzy name logic and Normalisation are for Age Verification only, or Match as well? (Toshi KDDI) + * It can apply not only for Age Verification, but also for Match, I think. (Huub KPN) + * In EU market, for Age Verification, it is needed to add some additional attributes like Name and Email, in order to identify User is Contractor. It is understood that Japan does not need them and wants to make them optional. Will propose some proposal based on today’s discussion. (Huub KPN) **AI #13.04 (Huub KPN)** + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + +* README.md should have Age Verification + * An Issue/PR is to be proposed. (AI #12.01) + +## AOB +* **Next meeting: 2024/5/14(Tue) 0900-1000 CEST.** +* According to the meeting cycle, the next meeting would be held on 2024/4/30(Tue), but Gilles Orange and Toshi KDDI will not be available on that date, meaning two of the three Codeowners will be unavailable, so Toshi proposed to skip the meeting on that day, adding that day (and the week) will be a Japanese holiday (week). The proposal was agreed. +* It was also agreed that GitHub discussion should continue, irrespective of the skip of the regular meeting. +* It was noted that KnowYourCustomer SP regular calls will be held on Zoom platform from the next meeting on 2024/5/14. + +## Action Items +* **AI#13.01**: Toshi will move remaining discussions in Issue #18 to a new Issue to be created for V0.2.0. [Toshi] +* **AI#13.02**: Toshi will move remaining discussions in Issue #22 to a new Issue to be created for V0.2.0. [Toshi] +* **AI#13.03**: Toshi will create Issues for each of the outstanding items listed in Issue #65. [Toshi] +* **AI#13.04**: Huub will share his Age Verification proposal based on discussions made during today’s meeting, with members as a GitHub comment. [Huub] +* **All other remaining AIs** + +[END] + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6b2183ead8c92a1c56b9ed1e6bb04070096acfd9 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14/raw.md @@ -0,0 +1,124 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-05-14 + +* Tuesday, May 14th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-04-16 draft; [PR #78](https://github.com/camaraproject/KnowYourCustomer/pull/78), created on April 26th. ->No comments and approved. +* Uploading the meeting 2024-04-16 material -> [PR #76](https://github.com/camaraproject/KnowYourCustomer/pull/76), has been approved and merged. +* Actions: + * Closed: AI #12.01, #13.04 + * Kept open: AI #06.06, #08.01, #08.02, #09.01, #11.01, #12.01, #13.01, #13.02, #13.03 +* Telefonica Fernando commented that he would like to discuss Match v0.1.1 which he had proposed. It was agreed to cover this topic during Match v0.1.0 agenda later. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions will be moved to a new issue for v0.2.0. AI #13.01 (Toshi) is still open. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0. AI #13.02 (Toshi) is still open. + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79))
        PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion + * Issue #79 and PR #80 were proposed by Telefonica. In KYC-Match v0.1.0, the example of 'country' attribute is "Japan" (name of country), but Telefonica would like to change it to one of Alpha-2 country codes. Device Status API (Roaming Status) uses Alpha-2 country codes, and Telefonica is implementing KYC-Match API with Alpha-2 country codes. (Telefonica Fernando) + * Fine with Orange. (Orange Gilles) + * May I suggest changing the attribute to 'countryCode' or something? (KDDI Toshi) + * Device Status API uses 'countryCode' attribute for MCC, so Telefonica would suggest using 'country' attribute to avoid potential confusion. Proposal is just to modify the example and not to touch the core v0.1.0 specification. (Telefonica Fernando) + * Fine with Orange. Scrutiny of country-related attributes should be addressed in v0.2.0 discussion. Orange thinks of using TM Forum format for that. (Orange Gilles) + * Agree to revisit this topic in v0.2.0 discussion. For example, Device Status API uses 'countryName' for Alpha-2 codes, and OIDF/OIDC specficications use 'countryCode' for Alpha-2 codes. (KDDI Toshi) + * As both Telefonica and Orange are implementing the Match v0.1.0, this matter should be concluded quickly. (Orange Gilles, Telefonica Fernando) + * It seems it could be agreed that KYC-Match v0.1.0 uses 'country' attribute for Alpha-2 codes and includes an example of Alpha-2 code. However, taking it into account that some members are absent, we could accept any comments within 24 hours if any. (KDDI Toshi) + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
        PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this Issue will be broken down to Issues for each item. (AI #13.03) + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + + * Ongoing discussion + * How to write address, how to separate address to several fields, are different for the Netherlands, Spain, and Japan. It is difficult. Continue discussion. + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Ongoing discussion + * The Netherlands has a unique way to manage First/Family names. If it is not used, Match rate will worsen. (KPN Huub) + * Telefonica would prefer small number of Attributes in the Match API. (Telefonica Fernando) + * Continue discussion. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * It seems we have almost completed our discussion on the point, so, now we need to clarify which items are mandatory and which items are optional. (Toshi KDDI) + * From KDDI point of view, Match scoring is not needed. (Toshi KDDI) + * Telefonica will discuss internally on whether Match scoring is needed or not. (Telefonica Fernando) + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. + +### Overall +* Issue #75 Select API for CAMARA Meta-Release September #75 ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing + * This issue will be discussed in the next meeting. + +## AOB +* **Next meeting: 2024/5/28(Tue) 0900-1000 CEST.** + +## Action Items +* **All remaining AIs** + +[END] + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..48b02669db754c484c6a07432d9aeb8f0b5e3306 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28/raw.md @@ -0,0 +1,160 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-05-28 + +* Tuesday, May 28th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Axel Nennker, DT +* Clara Serrano, Telefonica +* Jorge Garcia Hospital, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-05-14 draft; [PR #84](https://github.com/camaraproject/KnowYourCustomer/pull/84), created on May 22nd. ->No comments and approved. +* Uploading the meeting 2024-05-14 material; [PR #83](https://github.com/camaraproject/KnowYourCustomer/pull/783), created on May 21st ->No comments and approved. +* Actions: + * Closed: AI #08.01, #13.01, #13.03 + * Kept open: AI #06.06, #08.02, #09.01, #11.01, #13.02 + * Closure of AI #13.01 was confirmed in the related agenda later. + * AI #08.02, #09.01 and #11.01 are thought to be closed. To be checked by next meeting. + +* In relation to AI #08.02, Telefonica Clara shared their view that for Age Verification API, attributes other than Age should be made completely optional, because it may result in application developer’s confusion between Age Verification API and KYC Match API if Age Verification API’s request body has additional attributes e.g. name and email address. KDDI Toshi suggested to discuss this topic in the later Age Verification agenda as the moderator, and, from KDDI perspective, agreed with Telefonica’s view. + +## Review Issues & PRs + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing + * Need to fill in all the necessary items on the release-management template which exists in the KYC-SP’s wiki page. This is one of the steps required for the meta-release. (DT Axel) ->Will study to fill in. (KDDI Toshi) + +* Issue #92 Tenure API to be handled in KYC-SP regular meeting and ML ([Issue #92](https://github.com/camaraproject/KnowYourCustomer/issues/92)) + * Discussion ongoing + * There was no comment. Agreed that Tenure API will use KYC-SP regular meetings and KYC-SP ML + +* Match scoring enhancement was proposed through API Backlog API Backlog ([Issue #45](https://github.com/camaraproject/APIBacklog/issues/45) / ([PR #46](https://github.com/camaraproject/APIBacklog/pull/46) + * Discussion ongoing + * Toshi explained our situation that we have an issue for that, and that we are discussing it. Toshi understand we continue our discussion, taking the proposed template into consideration. Toshi pointed out that KYC Match API (enhanced or whatever it is called) should work without Scoring as some markets/operators/API users do not need Scoring, and that was endorsed by API Backlog WG. + * Related to Issue #85 + * Telefonica Clara commented that backward compatibility is required, as Telefonica has implemented KYC-Match v0.1.0. KDDI Toshi seconded that. + * Continue discussion on Issue #85. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * New item. Asked what members think? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) + * KDDI Toshi commented that his understand was that this API is related to Credit Scoring and Credit Scoring does not have much to do with KYC information. Taking KYC-SP’s workload (many APIs), he feels it is difficult for KYC-SP to include Telco Scoring API. + * Telefonica Jorge Garcia commented that Telco Scoring API has much to do with KYC, as it would use the same data/information for Scoring. + * Continue discussion. + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * It is understood that the remaining topics are covered in new Issue #87, so, we are going to close this issue. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue, but it is to be confirmed if this issue can be closed. + * Stefano's comment is expected. As Stefano is absent, KDDI Toshi will contact Stefano. **AI #15.01 (Toshi)** + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * This PR will be closed without being merged, as PR #61 has already been merged. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79))
        PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion + * Regarding Issue #79, Telefonica Fernando would like to confirm if this can be agreed on. + * KDDI Toshi replied that, as commented in Issue #79, KDDI could agree with this proposal on condition that country related parameters will be revisited for the next version. + * As Issue #79 has been agreed, we can move on to validate PR #80. KDDI Toshi sudggested to have PR #80 include YAML modification for Issue #82. + * Telefonica Fernando, who is the owner of PR #80, agreed. **AI #15.02 (Fernando)** + +* Issue #82 Abbreviation "OB" in parameter description ([Issue #82](https://github.com/camaraproject/KnowYourCustomer/issues/82)) + * Ongoing discussion: It is understood that the proposal can be agreed upon. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + * There have been some discussions on GitHub recently, but, as Huub is absent today, we cannot check what the discussions look like. + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * Telefonica Clara commented that, as for Age Verification API, Telefonica does not think additional attributes are necessary to check and score how different the end user seems from the contract owner, and that, if these attributes are added, they should be optional attributes and the API should work without these optional attributes and scoring function. Telefonica Clara is requested to input the comments into GitHub Issue. **AI #15.03 (Clara)** + * After seconding Telefonica’s comments, KDDI Toshi asked Orange Gilles to summarise the current conclusions of the Issue #46 discussion. Gilles agreed. **AI #15.04 (Gilles)** + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. +## AOB +* **Next meeting: 2024/6/11(Tue) 0900-1000 CEST, which will include Tenure API agenda.** + +## Action Items +* **AI#15.01**: KDDI Toshi will contact Stefano to see Stefano’s view on closure of Issue #22. [Toshi] +* **AI#15.02**: Telefonica Fernando will proceed with PR #80 for Issue #79 as well as Issue #82. [Fernando] +* **AI#15.03**: Telefonica Clara will write their comments to GitHub Issue #46 regarding Age Verification API’s additional attributes in request body and scoring in response. [Clara] +* **AI#15.04**: Orange Gilles will summarise the current conclusions of the Issue #46 discussion. [Gilles] +* **All remaining AIs** + +[END] + diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1add4b53583d1abb45e5e68b1d38f1a33c808707 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11/raw.md @@ -0,0 +1,227 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-06-11 + +* Tuesday, June 11th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica +* Jorge Garcia Hospital, Telefonica +* Kevin Scarr, Vodafone +* Ola Ajibola, GSMA + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-05-28 draft; [PR #94](https://github.com/camaraproject/KnowYourCustomer/pull/94), created on June 1st. ->No comments and approved. +* Uploading the meeting 2024-05-28 material; [PR #93](https://github.com/camaraproject/KnowYourCustomer/pull/93), created on May 28th ->No comments and approved. +* Actions: + * Closed: AI #08.02, #13.01, #15.02, #15.04 + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + + +## Review Issues & PRs + +### New +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th; Discussion ongoing. + * For KYC Match v0.2.0. + * Huub KPN explained his proposal, followed by some discussion. + * Huub KPN: Mobile connect KYC match has this feature, Netherland has this and very useful. Contracts are anonymous, so customer types are important. Prepaid users have to be careful to check identity through other means. What have been done in NL was to match minimum data. But discussion should be open for anti-fraud cases and so on. + * Huub KPN: Customer can check the data or at least get confirmation that it is prepaid. + * ?: No optional feature? MC spec has optional feature? + * Huub KPN: in MC, this spec is optional. In CAMARA, you should make it optional too. Some country is not interested, you might not want to share this information. In the EU market, there are obligation to identify customer irrespective of subscription type, but in NL very useful. + * Jorge TEF: Tenure API is also suggested. Is this the match, so data is provided from customer? + * Huub KPN: They normally check the identity of the user, everything to do with the use case of verifying the identity of a customer, Tenure is different, but can also help specify prepaid or postpaid + * Jorge TEF: Limit optionality of the API, so separate API is good. + * Huub KPN: there are some attributes that can’t be provided, at least add to KYC match the same as MC. + * Clara TEF: + * Huub KPN: Reliability of SIM card, etc. + * Clara TEF: What are the use cases of Tenure? + * Hubb KPN: simply want to know somebody is reliable, put data to a kind of risk engine. + * Clara KPN: independent from match. + Huub KPN: can be used for multi-factor authentication. Banks who check passports are less likely interested in match but more in Tenure. + Clara TEF: In Telefonica we know MC has this feature. Match is true/false while prepaid/pospaid/business is raw data. + Huub KPN: in enterprise police can find out later, so prepaid and business are different. That is a value I want to provide. + + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th; Discussion ongoing. + * For KYC Match v0.2.0. + * Gilles Orange explained his proposal, followed by some discussion. + * Gilles Orange: One enumeration for all attributes. + * Toshi KDDI: will ask Gilles for explanation offline. It is for next version? -> Gilles Orange: Yes. + * Clara TEF: is this for version2? -> Gilles Orange: Yes. + * Gilles Orange: all attributes provide at least enumeration, developer of API find it difficult unless common enumeration. I’ll try to propose implementation of swagger. + * Kevin Carr VDF: are you trying to declare one common enum, instead of enum under each attribute? -> Gilles Orange: Yes. + + +* Issue #97 update and review CODEOWNERS and MAINTAINERS.md file (Hrebert DT) ([Issue #97](https://github.com/camaraproject/KnowYourCustomer/issues/97)) +* PR #98 97 update and review codeowners and maintainersmd file (Hrebert DT) ([PR #98](https://github.com/camaraproject/KnowYourCustomer/pull/98)) + * For General/Admin. To follow Governance Issue #134; modify the codeowners file and add GitHub user IDs to the maintainers.md file + * Opened on June 10th, and **Approved already**. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing; no new comments + * Toshi commented that this is important issue for our Fall24 Meta-release and this will be discussed in the next meeting and later meetings. + * In Issue #85 discussion later, there was some discussion on Issue #75: Toshi KDDI commented that we do not have much time so he is thinking of making Match/Fill-in v0.1.x our Meta-release candidate. + * Jorge TEF: Meta-release should be s table. If some operators have already deployed, it would be so much better. So, try to add as much feature as possible. + * Toshi KDDI: Let’s discuss Meta-release in Issue #75. Did you Jorge suggest adding Match Scoring? + * Jorge TEF: Yes. + +* Issue #92 Tenure API to be handled in KYC-SP regular meeting and ML ([Issue #92](https://github.com/camaraproject/KnowYourCustomer/issues/92)) + * **To be closed**; Tenure API is now handled as part of KnowYourCustomer API family, as TSC decided. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) ) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) ) + * Ongoing in API Backlog WG + + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * **Closed** + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. Can this issue be closed? + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * **Closed without being merged**, as already merged PR #61 covered the same issue. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79)) + * **Closed** as completed. +* PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion – let's proceed with this RP including Issue #82. + * -> PR modified to cover Issue #82, and then **approved and merged** (for both Match and Fill-in) +* Issue #82 Abbreviation "OB" in parameter description ([Issue #82](https://github.com/camaraproject/KnowYourCustomer/issues/82)) + * **Closed** as completed. + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + * Clara Telefonica commented, followed by some discussion: + * Clara TEF: Mostly acceptable proposal. Telefonica has already implemented this v0.1, so need backward compatibility. Telefonica would here propose not to enforce additional attribute for score, not to change attributes or objects, thus Scoring will not impact existing implementation. Otherwise fine. + * Kevin Carr VDF: Agree. Straightforward for developers to use. + * Gilles Orange: Understand that backward compatibility is strongly needed. + * Toshi KDDI: KDDI’s information is close to v0.1, so KDDI has the same position. + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + * Axel DT commented. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing; Gille's summary appreciated. + * Toshi KDDI commented "is it going to be Meta release? Almost ready for PR discussion?", after which there was some discussion: + * Clara TEF: just mentioning additional attributes in order to validate user, our objective. We only have data birthdate of contract owner, which is reality. We would like to have this info for all user, ambition, not reality. Something we may be able to have in future. Having these attributes mandatory will be in future. + * Huub KPN: one suggestion, we can make it entirely optional. Reflect score on the reliability of the data. We analyzed 30% of the end user are not contract owner, so with no data, we probably return 70%, it is not very reliable. + * Clara TEF: same, even higher. We don’t have all data, even Legal asked us to filter some data. + * Huub KPN: you can also provide very low score, in case if legal says. + * Clara TEF: + * Huub KPN: for example, if only family name is provided, reliability is now 70% to 85%. That’s how you can play with aggregate score, still useful for some use cases, and not mandating any attributes. + * Huub KPN: additional attributes can be optional. + * Clara TEF: I will provide comments to the issue. + * Toshi KDDI: we have enough discussion for ver0.1 on validating user/contact owner. Any additional feature? Let’s wait for Telefonica comments, and then move on to PR discussion. + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* Discussion not yet started, so skipped today. + * Clara Telefonica made a question, followed by some discussion: + * Clara TEF: Question. This API is not to give how long this customer has been a customer of this operator. In some comments, mentioning contract, MSISDN has been assigned to that user, then what exactly does operator have to check data? How long the customer has been in place? It is understood that UK has this API. + * Kevin Carr VDF: it is checking how long this number has been managed, MSISDN has been used, when that number joined to that network. Recycle is another API. + * Hubb KPN: need to be very clear about it, contract to end user? If contract is changed from business to personal to keep that number after leaving the company? + * Clara TEF: if new carrier, then zero? + * Huub KPN: if same carrier, Telefonica, do you reset? That is question we need to answer. + * Toshi KDDI: Details should be discussed anyway. + * Huub KPN: will comment. + + +## AOB +* **Next meeting: 2024/6/25(Tue) 0900-1000 CEST** + +## Action Items +* **No additional AIs from meeting #16** +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1e8820a43344ad6bfb7e7a691fcabd439d92ea63 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25/raw.md @@ -0,0 +1,210 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-06-25 + +* Tuesday, June 25th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica +* Kevin Scarr, Vodafone +* Ola Ajibola, GSMA + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-06-11 draft**; [PR #102](https://github.com/camaraproject/KnowYourCustomer/pull/102), created on June 20th. ->**[06/25]** No comments and approved. To be merged after the meeting. +* **Uploading the meeting 2024-06-11 material**; [PR #99](https://github.com/camaraproject/KnowYourCustomer/pull/99), created on June 11th ->Merged and document uploaded already. +* Actions: + * Closed: None + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + + +## Review Issues & PRs + +### New +* **Issue #100 Release v0.1.1 (Fernando TEF) [Merged]** ([PR #100](https://github.com/camaraproject/KnowYourCustomer/pull/100)) + * Opened on June 13thh; approved and merged + * Create release branch for KYC Match/Fill-in v0.1.1 and include CHANGLOG.md. (The approved PR #80 has already created v0.1.1 YAML.) + * **[06/25]** v0.1.1 is only for minor updates including modification of country field example, and v0.1.1 content itself had been updated by PR #80. This PR #100 is just for version number change and Changelog update. + +* **Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA)** ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * **[06/25]** Ola GSMA: At least any one property must be included in the request body? + * ->Toshi KDDI: the request body needs at least one property, which will be checked with the MNO's data. phoneNumber, i.e. identity, is also needed as mandatory, isn't it? + * ->Fernando TEF) phoneNumber could be retrieved from Access Token, so, at least one property must be included, in addition to phoneNumber. + * ->Fernando TEF) That will be documented in the next update. + * ->Toshi KDDI) OK. Toshi will write the comment to GitHub Issue #101. **AI#17.01 (Toshi)** + +* **PR #103 Align yaml with commonalities v0.3 (Fernando TEF)** ([PR #103](https://github.com/camaraproject/KnowYourCustomer/pull/103)) + * Opened on June 20th; Discussion ongoing + * For KYC Match/Fill-in v0.1.1? + * Align with commonalities v0.3. How about v0.4? + * **[06/25]** **Agreed, as aliment with the Commonalities items is mandatory for Meta-release.** + * Toshi KDDI: It is understood that v0.4 is coming separatly. Correct? ->Fernande TEF: Correct. v0.4 is mandatory for Fall24 Meta-release. + +* **PR #104 Include score functionality proposal (Fernando TEF)** ([PR #104](https://github.com/camaraproject/KnowYourCustomer/pull/104)) + * Opened on June 20th ; Discussion ongoing. For Match v0.2.0. + * To fix ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85) ([KYC Match] Scoring) and ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) (Create a common enum for attributeMatch result) + * **[06/25]** Clara TEF: Telefoncia's YAML proposal. Comments are welcome. This PR includes the above two issues. + * ->Toshi KDDI: Need some time to check the yaml. + * Toshi KDDI: One comment is, as commented in Issue #85, that scoring algorithm should not be mandatory, because there may be more suitable algorithm existing for each country and each language. + * ->TEF: If algorithm is different from countries and languages, the same request may receive different scoring results, which will be an issue. + * ->Kevin Scarr VDF: Jaro-Winkler algorithm has not been used for other languages than European langages. Send link to a website to Toshi. + * Here is the link to the security website that has Jaro-Winkler already implemented. + * https://asecuritysite.com/hashsim/simstring + * Toshi KDDI: In the first place, do we need to specify this kind of algorithm in the API specification? + * ->TEF: It is needed for Developers' understanding. + * ->Toshi KDDI: Then, how about making Jaro-Winkler algorithm as recommendation or as guideline for European language or Europe countries, but keeping algorithm TBD for other languages and countries? + * ->Kevin Scarr VDF) How about writing this sentence in the specification? Proposed: "Unless otherwise captured in the specification, score will use the Jaro-Winkler distance algorithm for all countries." + * ->Toshi KDD: Sounds agreeable. + * ->Clara TEF: Please try Jaro-Winkler algorithm with KDDI's data to find if it works for Japanese language. + * ->Toshi KDDI: I am no quite sure if we can do that, as we do not provide Match Scoring now, but I will discuss internally about trying it. **AI #17.01 (Toshi)** + * Gilles Orange: Orange proposed another endpoint for Match Scoring. + * ->TEF: It is better to have only one endpoint for KYC Match. + * TEF: Telefonica wants to include Match Scoring in Fall24 Meta-release. How will we proceed with this proposal? + * ->Toshi KDDI: Taking Meta-release schedule into account, I understand we have to proceed rapidly. ** Keep this discussion open until our next meeting on 9th July, and next meeting is the target to clear issues.** Let's continue discussion on GitHub. + * ->** Agreed. ** + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing; There were comments to propose KYC Match v0.2 with Scoring + * Thoughts: + * KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)? + * KYC Fill-in v0.1 (initial)? + *Age Verification v0.1 (initial)? + * **[06/25]** Toshi KDDI: Please comment to Issue #75, if any. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) ) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) ) + * Ongoing in API Backlog WG + * **In API Backlog June 13th, Jorge TEF and Toshi KDDI agreed that Telco Scoring API does not fit with KYC-SP. ->Telco Scoring API will not be a KYC Family API. Any objection?** + * **[06/25]** Toshi KDDI: Please send an email or contact to Toshi by next API Backlog WG meeting on June 27th, if you have any comment. **AI#17.02 (All)** + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing; Gille's summary appreciated. + * **[06/25]** Toshi KDDI: commented in Issue #46. If age verification true/false is needed and scoring is not needed, what will be the mandatory parameters? + * ->Gilles Orange: Age only. phoneNumber is optional. + * Toshi KDDI: It is understood that Age Verification v0.1.0 is candidate for Fall24 Meta-release. But, which should be prioritised, Age Verification or Match Scoring? + * ->Clara TEF: Match Scoring should be priortised, though it is not meant to stop Age Verification. + * ->Toshi KDDI: If other members agree with it, from KYC-SP point of view, it is OK. But Age Verification API is a GSMA Drop #3 API and from GSMA point of view, it is expected to be completed as early as possible. From KDDI side, Age Verification is an important one and early completion is expected. + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + +### Tenure v0.1.0 + +* Discussion not yet started, so skipped today. + +## AOB +* **Next meeting: 2024/7/9(Tue) 0900-1000 CEST** + +* **Planned Meetings:** toward Fall24 Meta-release, we plan to keep the cadence. + * #19 July 23rd, + * #20 August 6th, + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + +## Action Items +* **No additional AIs from meeting #16** +* **AI#17.01**: Toshi KDDI will write the comment to GitHub Issue #101 based on the discussion. [Toshi] +* **AI#17.02**: All is requested to send an email or contact to Toshi by next API Backlog WG meeting on June 27th, if you have any comment to the API Backlog's current conclusion that Telco Scoring API will not be a KYC Family API. [All] +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e55c0ea5b63270bb5c6a045bc457766f32b60d9c --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09/raw.md @@ -0,0 +1,190 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-07-09 + +* Tuesday, July 9th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, TEF +* Jorge Garcia Hospital, TEF +* Kevin Scarr, Vodafone + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-06-25 draft**; [PR #106](https://github.com/camaraproject/KnowYourCustomer/pull/106), created on July 2nd. ->**[July 9th]** No comments and approved. To be merged after the meeting. +* **Uploading the meeting 2024-06-25 material**; [PR #105](https://github.com/camaraproject/KnowYourCustomer/pull/105), created on June 27th ->Merged and document uploaded already. +* Actions: + * Closed: AI #17.01, #17.02 + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + * [July 9th] Agreed to close AI #09.01, #11.01 + +## Review Issues & PRs + +### New +* No new Issues/PRs except last meeting MoM and Agenda document. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * To be confirmed + * KYC Match v0.2 (v0.1 initial + v0.2 adds scoring) + * KYC Fill-in v0.1 (initial) + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **[July 9th]** No specific comment was raised during the meeting. The above was confirmed as current KYC-SP’s target for Fall24 Meta-release. + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* **Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA)** ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + * **[July 9th]** Clara and Jorge Telefonica ar ok with Toshi's comment on GitHub, but it is better to wait for Gilles and Fernando's check. Toshi will reach out to them. **AI#18.01 (Toshi)** + +* **PR #103 Align yaml with commonalities v0.3 (Fernando TEF)** ([PR #103](https://github.com/camaraproject/KnowYourCustomer/pull/103)) + * Opened on June 20th; Discussion ongoing + * For KYC Match/Fill-in v0.1.1? + * Discussed in Meeting 2024/06/25. **If no further comment, this will be approved and merged.** + * **[July 9th]** Approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. **AI#18.02 (Toshi)** + + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* **PR #104 Include score functionality proposal (Fernando TEF)** ([PR #104](https://github.com/camaraproject/KnowYourCustomer/pull/104)) + * Opened on June 20th ; Discussion ongoing. + * For Match v0.2.0. + * To fix ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85) ([KYC Match] Scoring) and ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) (Create a common enum for attributeMatch result) + * **[July 9th]** Approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. **AI #18.03 (Toshi)** + * Jorge and Clara TEF: as Fernando is on leave, codeowners are requested to merge PR #103 and PR #104. (Toshi will do.) Then, Telefonica will take care of further PRs toward Meta-release. For example, Commonalities v0.4 for Fall24 Meta-release. + * (Related to Issue #75) Toshi showed API readiness checklist on Release Management Wiki page, and shared his view that the following items should be worked on specifically; No.2 Design guidelines from Commonalities applied (v0.4), No.3 Guidelines from ICM applied (v0.2), and No.7 Basic API test cases & documentation. Other items are covered by usual API specification work or not needed as optional. Also, all required items shall be done by M4 August 31st, and release-candidate shall be ready then. + * Jorge TEF: agreed to start the necessary work as a basis, asked by Toshi KDDI. Thank you. + * Jorge TEF: also agreed to enter kyc-fill-in v0.1 into API Release Tracking, asked by Toshi KDDI. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* Toshi's observertion of current situation on Tenure API repo is briefed on page 14 of the meeting material. +* **[July 9th]**: It seems discussion not yet started, so skipped today. +* Clara TEF: TEF would like to prioritize Tenure API. +* Toshi KDDI: Noted. But, in API Backlog WG, it is being discussed how to proceed with these three APIs which have some common aspects, though start of Tenure API work in KYC SP has been approved by TSC. In addition, Tenure API lead is not identified. So, it is likely that eventually Tenure API will go on track. +* Kevin Scarr VDF: will contact Vodafone's Tenure member (Saker) to find out Tenure lead. **AI #18.04 (Kevin Scarr VDF)** + + +## AOB +* **Next meeting: 2024/July/23rd(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #20 August 6th, + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + + +## Action Items + +* **AI#18.01**: Clara and Jorge Telefonica are ok with Toshi's comment on GitHub, but it is better to wait for Gilles and Fernando's check. Toshi will reach out to them. [Toshi KDDI] +* **AI#18.02**: PR #103 Align yaml with commonalities v0.3 was approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. [Toshi KDDI] +* **AI#18.03**: PR #104 Include score functionality proposal was approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave.[Toshi KDDI] +* **AI#18.04**: Kevin Scarr VDF will contact Vodafone's Tenure member (Saker) to find out Tenure lead. [Kevin Scarr VDF] +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c510a8e597cec7d9b71a53eaeb68ac39d9411f34 --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23/raw.md @@ -0,0 +1,213 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-07-23 + +* Tuesday, July 23rd, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Clara Serrano, TEF +* Jorge Garcia Hospital, TEF +* Kevin Scarr, Vodafone +* Luis Lopez, Vodafone +* George, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-07-09 draft**; [PR #113](https://github.com/camaraproject/KnowYourCustomer/pull/113), created on July 12th.
        ->**[July 23rd]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-07-09 material**; [PR #110](https://github.com/camaraproject/KnowYourCustomer/pull/110), created on July 10th
        ->Merged and document uploaded already. + +* Actions: + * Closed: AI #18.02, #18.03 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, + * **[July 23rd]** Agreed to close AI #18.04, as Kevin Scarr VDF confirmedt that Luis Lopez VDF is the Tenure API lead, adding Kevin Scarr will also join the Tenure API discussion as a technical staff. + +## Review Issues & PRs + +### New + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) + * Opened on 2024/07/22. For both Match and Fill-in. + * **[July 23rd]** This PR is for alignment with Commonalities v0.4, and needs to be approved and merged for Meta-release Fall24. + * Together with PR #115 and PR #111, this needs to be approved and merged within this week, in order to meet Meta-release Fall24 M3 deadline.
        ->To meet this deadline, **this PR should be reviewed within 48 hours after the meeting ends**. +
        -> **All to review the PR #114 by 48 hours after the meeting ends.** **AI #19.01 (All)** + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) + * Opened on 2024/07/22. + * For Match only. Is the same content required for Fill-in? + * **[July 23rd]** This PR proposes to add Device Object-related requirements to the API specification, however, the proposal has not been approved in Commonalities, so, this PR need not be approved and merged for Meta-release Fall24 from the perspective of Commonalities alignment. Commonalities WG is supposed to approve this proposal for Mete-release Spring25, so, we could postpone this proposal till Spring25 as well. + * Jorge TEF: we should decide this to be approved and merged or not, by end of this week, to meet Fall24 Meta-release M3 deadline. +
        -> Toshi KDDI: Is it possible for us to make the preliminal decidion by end of this week, and then to correct it by a PR by M4 deadline, if needed? +
        -> Jorge TEF: That would not be a simple correction, so, it is not possible. +
        -> Toshi KDDI: Understood. Let's open for comments for 48 hours after the meeting ends, and then decide. +
        -> **All to review the PR #115 by 48 hours after the meeting ends.** **AI #19.02 (All)** + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) + * Opened on 2024/07/23. + * Corresponding to Issue #104 for Match. + * **[July 23rd]** This PR is to proceed with Fill-in API Fall 24 Mete-release, same as Match v0.2. +
        ->Jorge TEF: Version number needs to be changed from v0.1 to v0.1-rc1, as Herbert pointed out. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + * **[July 23rd]** This PR is for creation of Mete-release RC (Release Candidate), and needs to be approved and merged for Meta-release Fall24. + * Together with PR #115 and PR #114, this needs to be approved and merged within this week, in order to meet Meta-release Fall24 M3 deadline. To meet this deadline, **this PR should be reviewed within 48 hours after the meeting ends**. +
        -> **All to review the PR #111 by 48 hours after the meeting ends.** **AI #19.03 (All)** + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **[July 23rd]** Jorge TEF: There are two points to be decided today.
        (1) MatchScoreResult integer or float,
        (2) Scoring provides numbers only, and how to understand numbers is left to developers, assuming Jaro-Winkler algorithm is used. + * **(1) Agreed: interger.**
        -> Huub KPN: ok for interger, if it is KYC SP's decision. However, from KPN's experience of Mobile Connect, it may be changed to float in future. + * **(2) Agreed: Scoring provides numbers only.**
        ->Huub KPN: KPN is providing Match Scoring, and KPN leaves it (how to understand numbers) to customers (developers, API users), because requirements are different from each customer. KPN provides some supporting documents which are not included in API description. Regarding Normalisation, it should be done locally (by each country / operator), as it is different from countries and langugages. + * Geroge DT: who joined the meeting for the first time, made some questions on Match Scoring, Privacy issues and so on, which were answered by KYC SP members. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* **[July 23rd]** No discussion on Tenure API, as there was not enough time remaining. +* Clara TEF: TEF would like to focus on Tenure API once KYC Match v0.2 is closed. +* Toshi KDDI: Noted. But it will be contribution driven. KDDI would like to focus on Age Verification and Number Recycling which is new. + + +## AOB +* **Next meeting: 2024/August/6th(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + * #24 October 1st + +## Action Items + +* **AI#19.01**: All to review the PR #114 by 48 hours after the meeting ends. [All] +* **AI#19.02**: All to review the PR #115 by 48 hours after the meeting ends. [All] +* **AI#19.03**: All to review the PR #111 by 48 hours after the meeting ends. [All] +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..07713b881c7d413499816a18a1fe87876fda7aba --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06/raw.md @@ -0,0 +1,297 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-08-06 + +* Tuesday, August 6th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, TEF +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Axel Nennker, DT +* Clara Serrano, TEF +* Ola Ajibola, GSMA +* Luis Lopez, Vodafone +* Kenichi Yamamoto, KDDI [New] +* Guan-Han Ma, Chunghwa Telecom [New] +* Masaharu Hattori, KDDI [New] +* Frank Tsai, Chunghwa Telecom [New] + +Four new contributors and a new company, Chunghwa Telecom (Taiwan), were welcomed. + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-07-23 draft**; [PR #128](https://github.com/camaraproject/KnowYourCustomer/pull/128), created on August 3rd.
        ->**[August 6th]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-07-23 material**; [PR #127](https://github.com/camaraproject/KnowYourCustomer/pull/127), created on August 2nd
        ->Merged and document uploaded already. + +* Actions: + * Closed: AI #19.01, #19.02, #19.03 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, + + +## Review Issues & PRs + +### General - Meta-release overall status was reviewed first. +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + * **[August 6th]** API Release Trackers were reviewed; [Match](https://wiki.camaraproject.org/display/CAM/kyc-match+v0.2.0), [Fill-in](https://wiki.camaraproject.org/display/CAM/kyc-fill-in+v0.1.1) + * Release Issue was reviewed; [Issue #68](https://github.com/camaraproject/ReleaseManagement/issues/68) KnowYourCustomer r1.1 release review + * Remaining items; Test files should be made available. +
        ->Toshi) By when, we have to prepare them? +
        ->Rafal)Will check, during the meeting, hopefully. +
        ->Fernando) Will take care of Match test file, but not Fill-in test file. +
        ->Toshi) Is supposed to take care of Fill-in test file. +
        ->Toshi) Asked Fernando if he have started preparing Match test file, considering copying it to create Fill-in test file? +
        ->Fernando) replied not yet, but mentioned he has created SIM Swap test files, so he can create Match test file in the same way, and as Match is Initial release, it would be easier. + * **After the meeting**, Rafal emailed Fall24 Meta-release schedule to KYC-SP ML. +
        ->According to this, it is understood: + * that we can put 'tbd' for test files in the Readiness Checklist in the meantime + * that we have to prepare test files by M4 deadline, i.e. August 26th. + + + +### New + +* **Issue #117 [KYC Match / KYC Fill-in] givenName appears as giventName in specification examples / Toyeeb GSMA** ([Issue #117](https://github.com/camaraproject/KnowYourCustomer/issues/117)) + * Opened on 2024/07/25. For both Match and Fill-in. + * Corrections: giventName -> givenName, added Scoring response example float -> integer + * Already covered by PR #119, so, **this issue can be closed**. + +* **PR #118 Create API-Readiness-Checklist_kyc-fill-in / Toshi KDDI** ([PR #118](https://github.com/camaraproject/KnowYourCustomer/pull/118)) + * Opened on 2024/07/25. For Fill-in Meta-release. **Approved and merged on 2024/07/26.** + +* **PR #119 Pre release r1.1 for kyc-match + kyc-fill-in + CHANGELOG + README / Fernando TEF** ([PR #119](https://github.com/camaraproject/KnowYourCustomer/pull/119)) + * Opened on 2024/07/26 + * For Fall24 Meta-release candidate creation. Still open. + * KYC Fill-in version changed from v0.1.1 to v0.2.0, according to Herbert’s suggestion. + + +* **Issue #120 [kyc-match]: gender-example in the request is not aligned with the gender-enum / maxl2287** ([Issue #120](https://github.com/camaraproject/KnowYourCustomer/issues/120)) + * Opened on 2024/07/29. + * Gender example modified from Uppercase to lower case. Fixed by [PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121), and **Closed**. + + +* **PR #121 [kyc-match]: Uppercase gender-value in request-example / maxl2287** ([PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121)) + * Opened on 2024/07/29. For Issue #120. Approved and merged on 2024/07/30. + * **[August 6th]** Toshi KDDI) Maxl2287/ Maximilian is not in today, but does anybody know which company Maxl2287/ Maximilian is from? +
        ->Rafal DT) DT, development side. + + +* **Discussion #122 What to expect for Hankaku & Zenkaku? / maxl2287** ([Discussion #122](https://github.com/camaraproject/KnowYourCustomer/discussions/122)) + * Opened on 2024/07/31. + * **[August 6th]** Toshi KDDI) has answered to his question. Hope he would be happy. + + +* **PR #123 KYC-Match: IdDocument type / Ramesh SpryFox** ([PR #123](https://github.com/camaraproject/KnowYourCustomer/pull/123)) + * Opened on 2024/08/01. + * **[August 6th]** Toshi KDDI) Fernando, have you looked at this PR? Can this PR be included in Fall24 Meta-release as correction, or is this for next releases as Enhancement? +
        ->Fernando TEF) This PR should be for next releases. +
        ->Huub KPN) This topic is very complex, so much discussion will be needed. +
        ->**Agreed to work on this PR for future releases.** +
        ->Toshi KDDI) will note as GitHub comment. **AI #20.01 (Toshi KDDI)** + + +* **Issue #124 KYC-Match: Matches the subscriber or phone user data? / Ramesh SpryFox** ([Issue #124](https://github.com/camaraproject/KnowYourCustomer/issues/124)) + * Opened on 2024/08/01. + * Same as Issue #89. + * **[August 6th]** Agreed: To be discussed for next versions. + + +* **Issue #125 Align info.description Auth section with ICM 0.2.0 / Fernando TEF Issue #125** ([Issue #125](https://github.com/camaraproject/KnowYourCustomer/issues/125)) +* **PR #126 Align info.description Auth section with ICM 0.2.0 / Fernando TEF** ([PR #126](https://github.com/camaraproject/KnowYourCustomer/pull/126)) + * Opened on 2024/08/02 + * For Fall24 Meta-release, alignment to ICM v0.2.0, for both Match and Fill-in. + * **[August 6th]** Toshi KDDI) As this is for alignment with ICM v0.2.0, we should approved this. After the meeting, Toshi will approve this straightaway, so, would like Fernando to merge this without Gilles' approval as he is on holiday and the subproject approved this at the meeting anyway. +
        ->Fernando TEF) OK. + + +* **Issue #129 Fix images links in Yaml files / Fernando TEF** ([Issue #129](https://github.com/camaraproject/KnowYourCustomer/issues/129)) +* **PR #130 Update flow images links / Fernando TEF** ([PR #130](https://github.com/camaraproject/KnowYourCustomer/pull/130)) + * Opened on 2024/08/05 + * Correction. + * **[August 6th]** Toshi KDDI) he thought it was only for corrections of the links for the flow drawing file, but 'Files Changes' showed Line 13 (not relating to the link) as well. Commented to the PR in GitHub. +
        Fernando TEF) There was a correction of a typo. +
        Toshi KDDI) Now I found you had replied so in GitHub. Understood. Thank you. +
        ->Toshi KDDI) Then, after the meeting, Toshi will approve this straightaway, so, would like Fernando to merge this without Gilles' approval as he is on holiday and the subproject approved this at the meeting anyway. +
        ->Fernando TEF) OK. + + + +### Match/Fill-in v0.2.0 – For Fall24 Meta-release + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) + * Opened on 2024/07/22. For both Match and Fill-in. + * **Approved and merged** + + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) + * Opened on 2024/07/22. + * Discussed on 2024/07/23 meeting, and by comments within 48 hours, this PR has been postponed. + * But Fernando has revisited this PR. + * **[August 6th]** This PR is about the way to describe how to handle 'phoneNumber' in API Description, related to 3-legged Access Token. Commonalities' API Design Guidelines have had guide about how to handle Device Object but not yet handle phoneNumber, so, this PR includes text modified for KYC/phoneNumber by Rafal DT and Fernando TEF, based on SIM Swap's description. + * Toshi KDDI) As commented in GitHub PR, I would prefer to postpone it as it is not agreed by Commonalities. +
        -> Fernando and Clara TEF) will discuss internally in Telefonica and will comment to GitHub PR within today. +
        -> Rafal DT) also will discuss internally in DT by tomorrow morning. +
        -> Toshi KDDI) OK. Let's keep this PR open for comments within 24 hours after the meeting closed. +
        -> Huub KPN) This is related to API Misuse and Privacy issue in Commonalities. + * **All to re-review the PR #115 by 24 hours after the meeting ends.** **AI #20.02 (All)** + + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) + * Opened on 2024/07/23. + * Corresponding to Issue #104 for Match. + * PR #118 covers this issue, and PR #118 has been merged. + + + +### General - other than Fall24 Meta-release + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + * Conclusion: as in Issue #109 + + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) **Closed** + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) *Merged** + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **Can be closed, as we agreed with 'integer'.** + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* **[August 6th]** Clara TEF made a question, and there was some discussion about the question. +* Toshi KDDI) suggested that it would be better to create GitHub issues for recording and openness/transparency purposes. + + +## AOB +* **Next meeting: 2024/August/21st(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #22 September 3rd, + * #23 September 17th + * #24 October 1st + +## Action Items + +* **AI#20.01**: Toshi will write a comment to GitHub PR that it was agreed that PR #123 would be discussed for future releases. [Toshi] + +* **AI#20.02**: All to re-review the PR #115 by 24 hours after the meeting ends. [All] + +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5ac583904af35e0587484875f528a604a66ec17e --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20/raw.md @@ -0,0 +1,297 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-08-20 + +* Tuesday, August 20th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, TEF +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Jorge Garcia Hospital, TEF +* Ola Ajibola, GSMA +* Luis Lopez, Vodafone +* Masaharu Hattori, KDDI [New] + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-08-06 draft**; [PR #132](https://github.com/camaraproject/KnowYourCustomer/pull/132), created on August 13th.
        ->**[August 20th]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-08-06 material**; [PR #131](https://github.com/camaraproject/KnowYourCustomer/pull/131), created on August 7th
        ->Merged and document uploaded already. + +* Actions: + * Closed: AI #20.02 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, #20.01 + + +## Review Issues & PRs + +### General - Meta-release overall status was reviewed first. +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + * **[August 20th]** + * **Should test files be made available by M4 deadline (2024/08/26)?** +
        Yes, but it is unclear how strictly the deadline for test files will be applied, because there are many APIs that have not test files available yet. +
        Anyway, it was agreed to try to create test files by the deadline. Issues will be opened first. Fernando TEF for KYC Match, Toshi KDDI for KYC Fill-in. **AI #21.01 (Fernando TEF, Toshi KDDI)** + * **Do we have to create another PR for Release r1.1 or Meta-release, in addition to PR #119 Pre-release r1.1 which has been merged?** +
        Yes, Release PR is required. Release PR would have some differences from Pre-release PR; for example, Changelog, Checklist (test files "to be available" to "Yes"), etc. Release PR's deadline is August 26th. + * **after the meeting** Deadline for Release PR is August 26th, but the deadline for test files (and other release items) is August 30th, since Release PR is expected to get ready for approval/merging by August 30th. + + +### New + +* **Issue #133 KYC-match: When provider decides which information to not send - expected response/Output? / Natylee93** ([Issue #133](https://github.com/camaraproject/KnowYourCustomer/issues/133)) + * Opened on 2024/08/14. For Fill-in, not Match? + * **[August 20th]** Toshi has commented his answer for Fill-in. Natylee93's respose is awaited, as Natlee93 was not in, + +* **Issue #134 KYC Match : CountryMatchScore makes no sense / Huub KPN** ([Issue #134](https://github.com/camaraproject/KnowYourCustomer/issues/134)) + * Opened on 2024/08/14. + * For Match, as ‘Country’ has now become ISO 3166-1 alpha-2, countryMatchScore is not needed. +
        ->Makes sense. Can this be incorporated into Fall24 meta? + * **[August 20th]** Fernando TEF will open a PR for this Issue, to incorporate this into Meta release. **AI #21.02 (Fernando TEF)** + +* **Issue #135 [KYC Match] Which fields are meant to be used for identification of the mobile phone user? / Toyeeb GSMA** ([Issue #135](https://github.com/camaraproject/KnowYourCustomer/issues/135)) + * Opened on 2024/08/15. + * IdDocument related error. + * **[August 20th]** Fernando TEF will open a PR for this Issue, to incorporate this into Meta release. **AI #21.03 (Fernando TEF)** + + +* **Issue #136 Start using LF Confluence for agenda and minutes / Fernando** ([Issue #136](https://github.com/camaraproject/KnowYourCustomer/issues/136)) + * Opened on 2024/08/19. + * Subproject Management. + * **[August 20th]** Toshi will start using LF Confluence. This has been one of Toshi's actions for a while. After the current Meta-release rush, so probablly from next meeting. Maybe from this meeting's minutes, but unlikely. + + + +### General - other than Fall24 Meta-release **(No update)** + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + * Conclusion: as in Issue #109 + + + +### Match/Fill-in v0.1.0 – released version **(No update)** +* Release version v0.1.1 completed with some correction. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + + +### Match/Fill-in v0.2.0 + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) **(Closed)** + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) **(Merged)** + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **Can be closed, as we agreed with 'integer'.** + + + +### Match/Fill-in v0.2.0 – For Fall24 Meta-release + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) **(Merged)** + * Opened on 2024/07/22. For both Match and Fill-in. + + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) **(Open)** + * Opened on 2024/07/22. + * Discussed on 2024/07/23 meeting, and by comments within 48 hours, this PR has been postponed. + * Discussed on 2024/08/06 meeting, and by comments within 24 hours, this PR has been postponed. + * This PR/topic needs to be discussed right after the Fall24 Meta rush. This PR/topic is related to ‘handling of 3-legged token and device object’ topic, which is covered by Commonalities v0.4.0 (for Fall24 Meta), and API misuse topic, which is being discussed in Commonalities. + + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) **(Closed on 2024/08/19)** + * Opened on 2024/07/23. + * PR #118 covers this issue, and PR #118 has been merged. + + +* **Issue #117 [KYC Match / KYC Fill-in] givenName appears as giventName in specification examples / Toyeeb GSMA** ([Issue #117](https://github.com/camaraproject/KnowYourCustomer/issues/117)) **(Closed on 2024/08/19)** + * Opened on 2024/07/25. For both Match and Fill-in. + ** Already covered by PR #119, so, **this issue can be closed**. + + +* **PR #118 Create API-Readiness-Checklist_kyc-fill-in / Toshi KDDI** ([PR #118](https://github.com/camaraproject/KnowYourCustomer/pull/118)) **(Merged)** + * Opened on 2024/07/25. For Fill-in Meta-release. Approved and merged on 2024/07/26. + + +* **PR #119 Pre release r1.1 for kyc-match + kyc-fill-in + CHANGELOG + README / Fernando TEF** ([PR #119](https://github.com/camaraproject/KnowYourCustomer/pull/119)) **(Merged)** + * Opened on 2024/07/26 + * For Fall24 Meta-release candidate creation. Still open. + * KYC Fill-in version changed from v0.1.1 to v0.2.0, according to Herbert’s suggestion. + + +* **Issue #120 [kyc-match]: gender-example in the request is not aligned with the gender-enum / maxl2287** ([Issue #120](https://github.com/camaraproject/KnowYourCustomer/issues/120)) **(Closed)** + * Opened on 2024/07/29. + * Gender example modified from Uppercase to lower case. Fixed by [PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121), and **Closed**. + + +* **PR #121 [kyc-match]: Uppercase gender-value in request-example / maxl2287** ([PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121)) **(Merged)** + * Opened on 2024/07/29. For Issue #120. Approved and merged on 2024/07/30. + +* **Discussion #122 What to expect for Hankaku & Zenkaku? / maxl2287** ([Discussion #122](https://github.com/camaraproject/KnowYourCustomer/discussions/122)) **(Answered)** + * Opened on 2024/07/31. + + +* **PR #123 KYC-Match: IdDocument type / Ramesh SpryFox** ([PR #123](https://github.com/camaraproject/KnowYourCustomer/pull/123)) **(Enhancement)** + * Opened on 2024/08/01. + * Related to IDDocument type. Correction, or Enhancement/ + * Meeting on 2024/08/06 agreed that this issue is to be discussed for future versions. + * **[August 20th]** On GitHub, Huub and Axel replied, and Ramesh was satisfied. There was a question what responses are expected under the current spec. +
        Toshi confirmed at the meeting that true, false, not available. + + +* **Issue #124 KYC-Match: Matches the subscriber or phone user data? / Ramesh SpryFox** ([Issue #124](https://github.com/camaraproject/KnowYourCustomer/issues/124)) **(Enhancement)** + * Opened on 2024/08/01. + * Same as Issue #89. + * Meeting on 2024/08/06 agreed that this issue is to be discussed for future versions. + + +* **Issue #125 Align info.description Auth section with ICM 0.2.0 / Fernando TEF Issue #125** ([Issue #125](https://github.com/camaraproject/KnowYourCustomer/issues/125)) **(Closed)** +* **PR #126 Align info.description Auth section with ICM 0.2.0 / Fernando TEF** ([PR #126](https://github.com/camaraproject/KnowYourCustomer/pull/126)) **(Merged)** + * Opened on 2024/08/02 + * For Fall24 Meta-release, alignment to ICM v0.2.0, for both Match and Fill-in. + + +* **Issue #129 Fix images links in Yaml files / Fernando TEF** ([Issue #129](https://github.com/camaraproject/KnowYourCustomer/issues/129)) **(Closed)** +* **PR #130 Update flow images links / Fernando TEF** ([PR #130](https://github.com/camaraproject/KnowYourCustomer/pull/130)) **(Merged)** + * Opened on 2024/08/05 + * Correction. + + + +### Age Verification v0.1.0 – wip **(No update)** + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + + +### Tenure v0.1.0 + +* **[August 20th]** Luis Lopez VDF explained: there is not much progress, as members' return from summer holiday is awaited. + + + +## AOB +* **Next meeting: 2024/September/3rd(Tue) 0900-1000 CEST** + +* **Planned Meetings:** + * #23 September 17th + * #24 October 1st + * #25 October 15th + +* **EasyCLA** Please be informed that CAMARA easyCLA activation has been postponed to End of August. Please visit [EasyCLA test repo](https://github.com/camaraproject/EasyCLA) and test / initiate your CLA status. + + +## Action Items + +* **AI#21.01**: It was agreed to try to create test files by the deadline. Issues will be opened first. Fernando TEF for KYC Match, Toshi KDDI for KYC Fill-in. [Fernando TEF, Toshi KDDI] + +* **AI#21.02**: Fernando TEF will open a PR for Issue #134 (CountryMatchScore makes no sense), to incorporate this into Meta release. [Fernando TEF] + +* **AI#21.03**: Fernando TEF will open a PR for Issue #135 (Which fields are meant to be used for identification of the mobile phone user?), to incorporate this into Meta release. [Fernando TEF] + + +* **All remaining AIs** + +[END] diff --git a/marked/KnowYourCustomer/documentation/MeetingMinutes/README/raw.md b/marked/KnowYourCustomer/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomer/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomerAgeVerification/README/raw.md b/marked/KnowYourCustomerAgeVerification/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..370577a68bcc1cd410714b269d61f13dc7d52300 --- /dev/null +++ b/marked/KnowYourCustomerAgeVerification/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# KnowYourCustomerAgeVerification + +Sandbox API Repository to describe, develop, document, and test the KnowYourCustomerAgeVerification Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mYAzC) + +## Scope + +* Service API(s) “KnowYourCustomerAgeVerification” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases/tag/r1.3) (Fall25), with the following API versions: + * **kyc-age-verification v0.2.1** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerAgeVerification/blob/r1.3/code/API_definitions/kyc-age-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerAgeVerification/r1.3/code/API_definitions/kyc-age-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerAgeVerification/r1.3/code/API_definitions/kyc-age-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerAgeVerification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +* **Releases of the CAMARA KYC Age Verification API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification/raw.md b/marked/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e7d1d8754887375d50277283f1a573c5e57d5e8c --- /dev/null +++ b/marked/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification/raw.md @@ -0,0 +1,517 @@ +# kyc-age-verification + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Age Verification + + description: | + + # Summary + This API provides the customer with the ability to check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. + + # API functionality + + The API defines one service endpoint: + + - `POST /verify` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and checks if the age of the subscriber is older than the age threshold in the request. + Additionally, as optional function, provides (1) if age check is done against another form of official identification (Note) or not (verifiedStatus), (2) an overall score of how certain is the response using both information provided in the request and information that the Operator holds(identityMatchScore), (3) an indicator on whether the subscription has any kind of content lock (contentLock) and (4) an indicator on whether the subscription has any kind of parental control activated (parentalControl). + Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). [Required only in case a 2-legged flow has been agreed between API Provider and API Consumer following CAMARA directives; otherwise, phoneNumber must not be included] + - `ageThreshold`: The age threshold from which the age of the user must be compared. [Required] + - any of `idDocument`, `name`, `givenName`, `familyName`, `middleNames`, `familyNameAtBirth`, `birthdate`, `email`; additional subscriber's information to be checked in order to confirm that the subscriber is the contract's owner [Optional] + - `includeContentLock` and `includeParentalControl`: These two flags allow the API Client to indicate that the corresponding response properties `contentLock` and `parentalControl` should be returned. Its implementation is optional for the API Provider, so in such cases, these parameters will be ignored. [Optional] + + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `ageCheck`: Indicate 'true' when the age of the user is the same age or older than the age threshold (age >= age threshold), and 'false' if not (age < age threshold). Otherwise, 'not_available'. + - `verifiedStatus`: true if the information provided was checked against another form of official identification (Note), otherwise false. Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + - `identityMatchScore`: The overall score of identity information available in the Operator, information either provided in the request body comparing it to the one that the MNO holds or directly using internal MNO's information. It is optional for the Operator to return the Identity match score. + - `contentLock`: Indicates if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked). + - `parentalControl`: Indicates if the subscription associated with the phone number has any kind of parental control activated. + + ## Errors + + - If the authentication access token is not valid, a `401 UNAUTHENTICATED` error is returned + - If the API call contains a formatting or other any other syntactic error, a `400 INVALID_ARGUMENT` error is returned. + - If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API consumer has a valid access token that does not have the required scope to obtain Age Verification information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/KnowYourCustomerAgeVerification + +servers: + - url: "{apiRoot}/kyc-age-verification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Age Verification + description: Operations to verify the age of a user. + +paths: + /verify: + post: + tags: + - Age Verification + summary: Verify Age Threshold + description: | + Verify that the age of the subscriber associated with a phone number is equal to or greater than the specified age threshold value. + + As it is possible that the person holding the contract and the end-user of the subscription may not be the same, the endpoint also admits a list of optional properties to be included in the request to improve the identification. The response may optionally include the `identityMatchScore` property with a value that indicates how certain it is that the information returned relates to the person that the API Client is requesting. To increase the reliability of the information returned, the API Provider may include in the response the `verifiedStatus` property, indicating whether the identity information in its possession has been verified against an identification document legally accepted as an age verification document (Note). Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + If the API Client indicates request properties `includeContentLock` or `includeParentalControl` with value `true` and the API Provider implements this functionality, then the response will also include `contentLock` and `parentalControl` properties to indicate if the subscription has any kind of content filtering enabled. On the other hand, if the request properties are not included or the API Client specifies value `false`, then the response properties will not be returned. If the API Provider doesn't implement this functionality, request properties will be ignored and response properties won't be returned in any case. + operationId: verifyAge + security: + - openId: + - kyc-age-verification:verify + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyRequestBody' + examples: + Two-Legged Access Token Example: + value: + ageThreshold: 18 + phoneNumber: '+34629255833' # Note: Only required in case a 2-legged flow has been agreed between API Provider and API Consumer; otherwise, do not include phoneNumber + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@example.com" + includeContentLock: true + includeParentalControl: true + Three-Legged Access Token Example: + value: + ageThreshold: 18 + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@gmail.com" + includeContentLock: true + includeParentalControl: true + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyResponseBody' + examples: + KYC_200Example: + value: + ageCheck: "true" + verifiedStatus: true + identityMatchScore: 90 + contentLock: "false" + parentalControl: "true" + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + VerifyRequestBody: + type: "object" + description: Request to verify the age threshold provided. + required: + - ageThreshold + properties: + ageThreshold: + $ref: "#/components/schemas/AgeThreshold" + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + idDocument: + $ref: "#/components/schemas/IdDocument" + name: + $ref: "#/components/schemas/Name" + givenName: + $ref: "#/components/schemas/GivenName" + familyName: + $ref: "#/components/schemas/FamilyName" + middleNames: + $ref: "#/components/schemas/MiddleNames" + familyNameAtBirth: + $ref: "#/components/schemas/FamilyNameAtBirth" + birthdate: + $ref: "#/components/schemas/Birthdate" + email: + $ref: "#/components/schemas/Email" + includeContentLock: + $ref: "#/components/schemas/IncludeContentLock" + includeParentalControl: + $ref: "#/components/schemas/IncludeParentalControl" + + AgeThreshold: + type: "integer" + minimum: 0 + maximum: 120 + description: The age to be verified. The indicated range is a global definition of maximum and minimum values allowed to be requested. It is important to note that this range might be more restrictive in some implementations due to local regulations of a country i.e. A country does not allow to request for an age under 18. This limitation must be informed during the onboarding process. + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + IdDocument: + type: "string" + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + Name: + type: "string" + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + GivenName: + type: "string" + description: First/given name or compound first/given name of the customer. + + FamilyName: + type: "string" + description: Last name, family name, or surname of the customer. + + MiddleNames: + type: "string" + description: Middle name/s of the customer. + + FamilyNameAtBirth: + type: "string" + description: Last/family/sur- name at birth of the customer. + + Birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + Email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + IncludeContentLock: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `contentLock` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + IncludeParentalControl: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `parentalControl` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + VerifyResponseBody: + type: "object" + description: Response to an age verification request + required: + - ageCheck + properties: + ageCheck: + $ref: "#/components/schemas/AgeCheck" + verifiedStatus: + $ref: "#/components/schemas/VerifiedStatus" + identityMatchScore: + $ref: "#/components/schemas/IdentityMatchScore" + contentLock: + $ref: "#/components/schemas/ContentLock" + parentalControl: + $ref: "#/components/schemas/ParentalControl" + + AgeCheck: + type: "string" + description: Indicate `"true"` when the age of the user is the same age or older than the age threshold (age >= age threshold), and `"false"` if not (age < age threshold). If the API Provider doesn't have enough information to perform the validation, a `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + VerifiedStatus: + type: "boolean" + description: | + Indicate `true` if the information provided has been compared against information based on an identification document legally accepted as an age verification document (Note), otherwise indicate `false`. Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + IdentityMatchScore: + type: "integer" + minimum: 0 + maximum: 100 + description: The overall score of identity information available in the API Provider, information either provided in the request body comparing it to the one that the API Provider holds or directly using internal API Provider's information. It is optional for the API Provider to return the Identity match score. + + ContentLock: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked) and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ParentalControl: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of parental control activated and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ErrorInfo: + type: "object" + required: + - status + - code + - message + properties: + status: + type: "integer" + description: HTTP response status code + code: + type: "string" + description: A human-readable code to describe the error + message: + type: "string" + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token +``` diff --git a/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e492d1328feca8cca11f535024067a9b162f7805 --- /dev/null +++ b/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-age-verification v0.2.1 in release r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
        public | stable
        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-age-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-age-verification.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/kyc-age-verification_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/z4AzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story/raw.md b/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3ea309a6abd720cd4375e0f1cce39f68d5c88cff --- /dev/null +++ b/marked/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story/raw.md @@ -0,0 +1,10 @@ +# KYC Age Verification API User Story + +| **Item** | **Details** | +|------|---------| +|_**Summary**_ | As an application developer of an age-restricted site or application, I want to verifiy the age of an End-User with Subcriber's information held by the MNO.| +|_**Roles, Actors and Scope**_ | **Roles:** End-User
        **Actors:** API Provider, API Consumer
        **Scope:** Any mobile phone line (not limited to 4G, 5G)| +|_**Pre-condition**_ | The preconditions are listed below:
        1. The End-User has provided mandatory/optional information of its identity to API Consumer
        2. API Consumer has onboarded to API Provider's API
        3. API Consumer has API credentials
        4. Privacy legal base requirement has been agreed between parties (End-User privacy)
        5. | +|_**Activities/Steps**_ | **Starts when:** The API Consumer application server makes a request to the Age Verification service (API) with the age restricted value.
          **Ends when:** The API Provider service returns **_True_** if the age has been correctly verified else it returns **_False_**. Optionally the API Providers returns also an identityMatchScore, whether the data used has been verified, and whether a contentLock and parentalControl are in place. | +|_**Post-conditions**_ | The API Consumer can make decision to use the returned answer to follow-up its process. | +|_**Exceptions**_ | Several exceptions might occur during the KYC Age Verification API operations:
          • Unauthorized: Not valid credentials (e.g. use of already expired access token).
          • Not Found: The phone number provided is not managed by the API Provider.
          • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
          • | diff --git a/marked/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README/raw.md b/marked/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomerFill-in/README/raw.md b/marked/KnowYourCustomerFill-in/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..23b5aa71540e551a52defb59e34848cfaeda072f --- /dev/null +++ b/marked/KnowYourCustomerFill-in/README/raw.md @@ -0,0 +1,56 @@ + + + + + + + + + +# KnowYourCustomerFill-in + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomerFill-in Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYAzC) + +## Scope + +* Service API(s) “KnowYourCustomerFill-in” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * request and receive the information for a particular end user, which is on file (and verified) by the end user's Operator in their own KYC records, in order for the service provider (API consumer) to confirm the accuracy of the information and provide a specific service to the end user. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/KnowYourCustomerFill-in/releases/tag/r1.3) (Fall25), with the following API versions: + * **kyc-fill-in v0.4.1** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerFill-in/blob/r1.3/code/API_definitions/kyc-fill-in.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerFill-in/r1.3/code/API_definitions/kyc-fill-in.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerFill-in/r1.3/code/API_definitions/kyc-fill-in.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerFill-in/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerFill-in/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerFill-in/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + +* Note: **Releases of the KnowYourCustomerFill-in API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/KnowYourCustomerFill-in/code/API_definitions/README/raw.md b/marked/KnowYourCustomerFill-in/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/KnowYourCustomerFill-in/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in/raw.md b/marked/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f7de5c4d436c35e40748eba380c2591a9eae927a --- /dev/null +++ b/marked/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in/raw.md @@ -0,0 +1,544 @@ +# kyc-fill-in + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Fill-in + + description: | + + This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + ## API Functionality + + This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + + * To fill-in the user personal data during the digital registration of an account to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Fill-in_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + + * The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + + * For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + ### Special Scopes + + This API uses the following special scope `kyc-fill-in:set-all` which means that the API provider returns an API response as if all these scopes were specified in the scope value in the request: + + `kyc-fill-in:phoneNumber kyc-fill-in:idDocument kyc-fill-in:idDocumentType kyc-fill-in:idDocumentExpiryDate kyc-fill-in:name kyc-fill-in:givenName kyc-fill-in:familyName kyc-fill-in:nameKanaHankaku kyc-fill-in:nameKanaZenkaku kyc-fill-in:middleNames kyc-fill-in:familyNameAtBirth kyc-fill-in:address kyc-fill-in:streetName kyc-fill-in:streetNumber kyc-fill-in:postalCode kyc-fill-in:region kyc-fill-in:locality kyc-fill-in:country kyc-fill-in:houseNumberExtension kyc-fill-in:birthdate kyc-fill-in:email kyc-fill-in:gender kyc-fill-in:cityOfBirth kyc-fill-in:countryOfBirth kyc-fill-in:nationality` + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to request information related to an end user against the account data bound to their phone number. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/KnowYourCustomerFill-in + +servers: + - url: '{apiRoot}/kyc-fill-in/vwip' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Fill-in + description: Operations to provide information related to a customer identity stored the account data bound to the customer's phone number. + +paths: + /fill-in: + post: + tags: + - Fill-in + summary: Providing information related to a customer identity stored the account data bound to the customer's phone number. + + operationId: KYC_Fill-in + + security: + - openId: + - kyc-fill-in:set-all + - openId: + - kyc-fill-in:phoneNumber + - openId: + - kyc-fill-in:idDocument + - openId: + - kyc-fill-in:idDocumentType + - openId: + - kyc-fill-in:idDocumentExpiryDate + - openId: + - kyc-fill-in:name + - openId: + - kyc-fill-in:givenName + - openId: + - kyc-fill-in:familyName + - openId: + - kyc-fill-in:nameKanaHankaku + - openId: + - kyc-fill-in:nameKanaZenkaku + - openId: + - kyc-fill-in:middleNames + - openId: + - kyc-fill-in:familyNameAtBirth + - openId: + - kyc-fill-in:address + - openId: + - kyc-fill-in:streetName + - openId: + - kyc-fill-in:streetNumber + - openId: + - kyc-fill-in:postalCode + - openId: + - kyc-fill-in:region + - openId: + - kyc-fill-in:locality + - openId: + - kyc-fill-in:country + - openId: + - kyc-fill-in:houseNumberExtension + - openId: + - kyc-fill-in:birthdate + - openId: + - kyc-fill-in:email + - openId: + - kyc-fill-in:gender + - openId: + - kyc-fill-in:cityOfBirth + - openId: + - kyc-fill-in:countryOfBirth + - openId: + - kyc-fill-in:nationality + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_FillinRequest' + examples: + KYC_FillInBodyExample: + value: + {"phoneNumber": "+34629255833"} + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + + content: + application/json: + schema: + $ref: '#/components/schemas/KYC_FillinResponse' + examples: + KYC_Fillin200Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: '36' + birthdate: '1978-08-22' + email: abc@example.com + gender: MALE + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + KYC_FillinRequest: + type: object + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + KYC_FillinResponse: + type: object + properties: + + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the id_document of the customer stored on the Operator's system. + + idDocumentType: + type: string + enum: [passport, national_id_card, residence_permit, diplomatic_id, driver_licence, social_security_id, other] + description: Type of the official identity document provided. + + idDocumentExpiryDate: + type: string + format: date + description: Expiration date of the identity document (ISO 8601). + + name: + type: string + description: Complete name of the customer stored on the Operator's system. It is usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer on the Operator's system. + + familyName: + type: string + description: Last name, family name, or surname of the customer stored on the Operator's system. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + middleNames: + type: string + description: Middle name/s of the customer stored on the Operator's system. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer stored on the Operator's system. + + address: + type: string + description: Complete address of the customer stored on the Operator's system. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address on the Operator's system. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address on the Operator's system. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: The postal code or Zip code of the customer's address, stored on the Operator's system. + + region: + type: string + description: Region/prefecture of the customer's address, stored on the Operator's system. + + locality: + type: string + description: Locality of the customer's address, stored on the Operator's system. + + country: + type: string + description: Country of the customer's address stored on the Operator's system. Format ISO 3166-1 alpha-2. + + houseNumberExtension: + type: string + description: House number extension of the customer stored on the Operator's system. Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: Birthdate of the customer, in ISO 8601 calendar date format (YYYY-MM-DD), stored on the Operator's system. + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain), stored on the Operator's system. + + gender: + type: string + description: Gender of the customer stored on the Operator's system (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + cityOfBirth: + type: string + description: City where the customer was born. + + countryOfBirth: + type: string + description: Country where the customer was born. Format ISO 3166-1 alpha-2. + + nationality: + type: string + description: ISO 3166-1 alpha-2 code of the customer’s nationality. In the case a customer has more than one nationality, it is supposed to be the nationality related to the ID document provided in the match request. + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token +``` diff --git a/marked/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md b/marked/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f837f2947c4437abaf6904c2a3a23ffc0a966ef5 --- /dev/null +++ b/marked/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
            + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
            **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
            **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
            1. The Customer:User has provided mandatory information of their identity
            2. Application developer has onboarded to MNO API
            3. Application developer has API credentials
            4. Privacy legal base requirement has been solved (Customer privacy)
            | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
            **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
            | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
            • Unauthorized: Not valid credentials (e.g. use of already expired access token).
            • Not Found: The number provided is not managed by the MNO
            • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
            | + +

            + +**User Story: KYC Fill-In - Get identity information of customer** +
            + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
            **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
            **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
            1. The Customer:User has provided mandatory information of their identity
            2. Application developer has onboarded to MNO API
            3. Application developer has API credentials
            4. Privacy legal base requirement has been solved (Customer privacy)
            | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
            **Ends when:** The MNO service returns the identity information stored in its customer database.
            | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
            • Unauthorized: Not valid credentials (e.g. use of already expired access token).
            • Not Found: The number provided is not managed by the MNO
            • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
            | + + diff --git a/marked/KnowYourCustomerFill-in/documentation/API_documentation/README/raw.md b/marked/KnowYourCustomerFill-in/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomerFill-in/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ab68c136edb0ffeb3f4d45d37ef4fc99c09bd844 --- /dev/null +++ b/marked/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-fill-in 0.4.1 in release r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-fill-in.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-fill-in.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/d4AzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/KnowYourCustomerFill-in/documentation/SupportingDocuments/README/raw.md b/marked/KnowYourCustomerFill-in/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomerFill-in/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomerMatch/README/raw.md b/marked/KnowYourCustomerMatch/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..844c02ad18d6d6abc600215380ba1bfb6010be3c --- /dev/null +++ b/marked/KnowYourCustomerMatch/README/raw.md @@ -0,0 +1,55 @@ + + + + + + + + + +# KnowYourCustomerMatch + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomerMatch Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/80117795/Know+Your+Customer) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/EQAzC) + +## Scope + +* Service API(s) “KnowYourCustomerMatch” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * compare the information that the Service Provider (SP) has for a particular user with that on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/KnowYourCustomerMatch/releases/tag/r1.2) (Fall25), with the following API versions: + * **kyc-match v0.4.0** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerMatch/blob/r1.2/code/API_definitions/kyc-match.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerMatch/r1.2/code/API_definitions/kyc-match.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerMatch/r1.2/code/API_definitions/kyc-match.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerMatch/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerMatch/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerMatch/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + +* Note: **Releases of the KnowYourCustomerMatch API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/KnowYourCustomerMatch/code/API_definitions/README/raw.md b/marked/KnowYourCustomerMatch/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/KnowYourCustomerMatch/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/KnowYourCustomerMatch/code/API_definitions/kyc-match/raw.md b/marked/KnowYourCustomerMatch/code/API_definitions/kyc-match/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..39fbe1dda4ebd5c9d565802ef8d47985d742eae6 --- /dev/null +++ b/marked/KnowYourCustomerMatch/code/API_definitions/kyc-match/raw.md @@ -0,0 +1,700 @@ +# kyc-match + +```yaml +openapi: 3.0.3 +info: + title: Know Your Customer Match + + description: | + + This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + * **Match Score**: a numerical value that quantifies the similarity between two pieces of text based on the words they contain. This score is often used in various applications like text comparison, plagiarism detection, information retrieval, and natural language processing. The score typically reflects how well the words in one text match the words in another text. In the context of this API, this score will be used to determine how much does the input information looks like the information stored in the Operator's system. Unless otherwise captured in the implementation notes which Operators may publish, score will use the Jaro-Winkler distance algorithm for all countries. This parameter, as optional, will be returned depending on the capability of the Operator to calculate the scoring value. This means that not all Operators will implement this functionality or won't have the requested parameter available. It can happen that an Operator implements the score functionality but, for whatever reason, is not able to calculate it based on the client's input or the related stored information. For these cases, the score property related won't be returned in the response. + The range of score values is between "0" and "100", where higher scores indicate a higher similarity between the two compared parameters. + + ## API Functionality + + This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + + * To verify the user personal data during the digital registration of an account to a 3rd party service. + + * To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the account data bound to their phone number. + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + version: wip + x-camara-commonalities: 0.6 + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/KnowYourCustomerMatch + +servers: + - url: '{apiRoot}/kyc-match/v0.4' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Match + description: Operations to match a customer identity against the account data bound to their phone number. + +paths: + /match: + post: + tags: + - Match + summary: Matching a customer identity by checking a set of attributes related against the account data bound to their phone number. + description: |- + Verify matching of a number of attributes related to a customer identity against the verified data bound to their phone number in the Operator systems. Regardless of whether the `phoneNumber` is explicitly stated in the request body, at least one of the other fields must be provided, otherwise a `HTTP 400 - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION` error will be returned. + + The API will return the result of the matching process for each requested attribute. This means that the response will **only** contain the attributes for which validation has been requested. Possible values are: + - **true**: the attribute provided matches with the one in the Operator systems, which is equal to a `match_score` of 100. + - **false**: the attribute provided does not match with the one in the Operator systems. + - **not_available**: the attribute is not available to validate. + operationId: KYC_Match + + security: + - openId: + - kyc-match:match + + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchRequestBody' + examples: + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + Three-Legged Without Phone Number Example: + value: + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchResponse' + examples: + KYC_Match200Example: + value: + idDocumentMatch: 'true' + idDocumentTypeMatch: 'true' + idDocumentExpiryDateMatch: 'true' + nameMatch: 'true' + givenNameMatch: 'not_available' + familyNameMatch: 'not_available' + nameKanaHankakuMatch: 'true' + nameKanaZenkakuMatch: 'false' + middleNamesMatch: 'true' + familyNameAtBirthMatch: 'false' + familyNameAtBirthMatchScore: 90 + addressMatch: 'true' + streetNameMatch: 'true' + streetNumberMatch: 'true' + postalCodeMatch: 'true' + regionMatch: 'true' + localityMatch: 'not_available' + countryMatch: 'true' + houseNumberExtensionMatch: 'not_available' + birthdateMatch: 'false' + emailMatch: 'false' + emailMatchScore: 87 + genderMatch: 'false' + cityOfBirthMatch: 'false' + cityOfBirthMatchScore: 86 + countryOfBirthMatch: 'true' + nationalityMatch: 'true' + + '400': + $ref: '#/components/responses/Generic400' + + '401': + $ref: '#/components/responses/Generic401' + + '403': + $ref: '#/components/responses/Generic403' + + '404': + $ref: '#/components/responses/Generic404' + + '422': + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + KYC_MatchRequestBody: + type: object + description: Payload to validate the customer data. + + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + idDocumentType: + type: string + enum: [passport, national_id_card, residence_permit, diplomatic_id, driver_licence, social_security_id, other] + description: Type of the official identity document provided. + + idDocumentExpiryDate: + type: string + format: date + description: Expiration date of the identity document (ISO 8601). + + name: + type: string + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer. + + familyName: + type: string + description: Last name, family name, or surname of the customer. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan. + + middleNames: + type: string + description: Middle name/s of the customer. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer. + + address: + type: string + description: Complete address of the customer. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: Zip code or postal code + + region: + type: string + description: Region/prefecture of the customer's address + + locality: + type: string + description: Locality of the customer's address + + country: + type: string + description: Country of the customer's address. Format ISO 3166-1 alpha-2 + + houseNumberExtension: + type: string + description: Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + gender: + type: string + description: Gender of the customer (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + cityOfBirth: + type: string + description: City where the customer was born. + + countryOfBirth: + type: string + description: Country where the customer was born. Format ISO 3166-1 alpha-2. + + nationality: + type: string + description: ISO 3166-1 alpha-2 code of the customer’s nationality. In the case a customer has more than one nationality, it is supposed to be the nationality related to the ID document provided in the match request. + MatchResult: + type: string + description: | + true - the attribute provided matches with the one in the Operator systems, which is equal to a `match_score` of 100. + false - the attribute provided does not match with the one in the Operator systems. + not_available - the attribute is not available to validate. + enum: + - 'true' + - 'false' + - 'not_available' + + MatchScoreResult: + type: integer + description: | + Indicates the similarity score assigned to the input value when it does not exactly match the value stored in the operator's system. + This property shall only be returned when the value of the corresponding match field is `false`. + A perfect match with a score of 100 is indicated by `match` being 'true' and no `matchScore` is returned in this case. + minimum: 0 + maximum: 99 + + KYC_MatchResponse: + type: object + properties: + idDocumentMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether Id number associated to the ID document of the customer matches with the one on the Operator's system. + idDocumentTypeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether document type associated to the ID document of the customer matches with the one on the Operator's system. + idDocumentExpiryDateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether document expiration date associated to the ID document of the customer matches with the one on the Operator's system. + nameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the complete name of the customer matches with the one on the Operator's system. + nameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + givenNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether First name/given name of the customer matches with the one on the Operator's system. + givenNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether last name/ family name/ surname of the customer matches with the one on the Operator's system. + familyNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaHankakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Hankaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaHankakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaZenkakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Zenkaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaZenkakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + middleNamesMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the middle names of the customer matches with the one on the Operator's system. + middleNamesMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameAtBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the Family Name At Birth of the customer matches with the one on the Operator's system. + familyNameAtBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + addressMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete address of the customer matches with the one on the Operator's system. + addressMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street name of the customer matches with the one on the Operator's system. + streetNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNumberMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street number of the customer matches with the one on the Operator's system. + streetNumberMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + postalCodeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the postal code / zip code of the customer matches with the one on the Operator's system. + regionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the region of the customer's address matches with the one on the Operator's system. + regionMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + localityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the locality of the customer's address matches with the one on the Operator's system. + localityMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country of the customer's address matches with the one on the Operator's system. + houseNumberExtensionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the house number extension of the customer's address with the one on the Operator's system. + birthdateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the birthdate of the customer matches with the one on the Operator's system. + emailMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the email address of the customer matches with the one on the Operator's system. + emailMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + genderMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the gender of the customer matches with the one on the Operator's system. + cityOfBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the city at birth of the customer matches with the one on the Operator's system + cityOfBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryOfBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country at birth of the customer matches with the one on the Operator's system + nationalityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the nationality of the customer matches with the one on the Operator's system + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION: + description: Indicated param combination is invalid + value: + status: 400 + code: KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + message: Indicated parameter combination is invalid + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided +``` diff --git a/marked/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md b/marked/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f837f2947c4437abaf6904c2a3a23ffc0a966ef5 --- /dev/null +++ b/marked/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story/raw.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
            + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
            **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
            **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
            1. The Customer:User has provided mandatory information of their identity
            2. Application developer has onboarded to MNO API
            3. Application developer has API credentials
            4. Privacy legal base requirement has been solved (Customer privacy)
            | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
            **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
            | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
            • Unauthorized: Not valid credentials (e.g. use of already expired access token).
            • Not Found: The number provided is not managed by the MNO
            • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
            | + +

            + +**User Story: KYC Fill-In - Get identity information of customer** +
            + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
            **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
            **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
            1. The Customer:User has provided mandatory information of their identity
            2. Application developer has onboarded to MNO API
            3. Application developer has API credentials
            4. Privacy legal base requirement has been solved (Customer privacy)
            | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
            **Ends when:** The MNO service returns the identity information stored in its customer database.
            | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
            • Unauthorized: Not valid credentials (e.g. use of already expired access token).
            • Not Found: The number provided is not managed by the MNO
            • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
            | + + diff --git a/marked/KnowYourCustomerMatch/documentation/API_documentation/README/raw.md b/marked/KnowYourCustomerMatch/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomerMatch/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md b/marked/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8594976efd9615c814cd5ad6e8fdbad273528fa8 --- /dev/null +++ b/marked/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-match 0.4.0 in release r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-match.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-match.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/RwAzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/KnowYourCustomerMatch/documentation/SupportingDocuments/README/raw.md b/marked/KnowYourCustomerMatch/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/KnowYourCustomerMatch/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ModelAsAService/README/raw.md b/marked/ModelAsAService/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d9d8a26e34a4336e21c9a1523a62e09ec59370ed --- /dev/null +++ b/marked/ModelAsAService/README/raw.md @@ -0,0 +1,64 @@ + + + + + + + + + +# ModelAsAService + +Sandbox API Repository to describe, develop, document, and test the ModelAsAService Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/_4AjAw) + +## Scope + +* Service APIs “ModelAsAService” (see APIBacklog.md) +* MaaS (Model as a Services) refers to the packaging of AI models and their associated capabilities into reusable services, enabling users to quickly and efficiently build, deploy, monitor, and invoke models without the need to develop and maintain underlying foundational capabilities. +* The API provides the API consumer with the ability to: + * build and manage personalized Knowledge Bases (knowledge-base) + * quickly construct unique Q&A Assistant applications (qa-assistant-manage) + * provide Q&A services to the users of the application (qa-assistant-service) + * NOTE: more model services to be added. +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ModelAsAService/releases/tag/r1.2) (Fall25), with the following API versions: + * **knowledge-base v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/knowledge-base.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/knowledge-base.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/knowledge-base.yaml) + * **qa-assistant-manage v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/qa-assistant-manage.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-manage.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-manage.yaml) + * **qa-assistant-service v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/qa-assistant-service.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-service.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-service.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ModelAsAService/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ModelAsAService/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ModelAsAService/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly (odd weeks), Tuesday, 09:00 UTC (11:00 UTC+2, 17:00 UTC+8) + * [Join](https://teams.live.com/meet/9374614741908?p=QFhUf7b0SHZRdXSfA6) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/GpKaVSqC) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/ModelAsAService/code/API_definitions/README/raw.md b/marked/ModelAsAService/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/ModelAsAService/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/ModelAsAService/code/API_definitions/knowledge-base/raw.md b/marked/ModelAsAService/code/API_definitions/knowledge-base/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3007f292ae90952812f2932801c8428c75eb5618 --- /dev/null +++ b/marked/ModelAsAService/code/API_definitions/knowledge-base/raw.md @@ -0,0 +1,628 @@ +# knowledge-base + +```yaml +openapi: 3.0.3 +info: + title: Knowledge Base + description: >- + This API offers comprehensive CRUD (Create, Read, Update, Delete) management capabilities for the knowledge base, along with document uploading functionality. + It is designed to provide applications with standardized capabilities for knowledge content storage and management, supporting multi-format document storage, fine-grained permission control, and end-to-end traceability. + It is suitable for building knowledge-intensive systems (such as intelligent customer service platforms and enterprise document platforms) while ensuring compliance. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## API Functionality + + This API allows the API consumer to perform CRUD operations on the knowledge base hosted on the server. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scopes are required: + - knowledge-base:knowledge-bases:create - Create new knowledge bases + - knowledge-base:knowledge-bases:read - Read knowledge base entries + - knowledge-base:knowledge-bases:update - Update existing knowledge bases + - knowledge-base:knowledge-bases:delete - Delete knowledge bases + - knowledge-base:documents:update - Upload documents to knowledge bases + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/knowledge-base/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Knowledge Base + description: Knowledge base management + +paths: + /knowledge-bases: + post: + operationId: createKnowledgeBase + summary: Create a new knowledge base + description: | + Creates a new knowledge base with the provided metadata. + + **Key Features:** + - Initializes a new knowledge base container + - Stores name and description metadata + - Generates unique knowledgeBaseId + + **Key Rules:** + - Requires `name` field in request body + - Requires `knowledge-base:knowledge-bases:create` scope + - Name must be unique within the system + + **Response Characteristics:** + - **201 Created**: Returns full `KnowledgeBase` object with generated ID + - **400 Bad Request**: Missing `name` or invalid parameters + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Backend processing failure + tags: + - Knowledge Base + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:knowledge-bases:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBaseCreateRequest' + responses: + '201': + description: Knowledge base created successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + get: + operationId: listKnowledgeBases + summary: Get all knowledge bases + description: | + Retrieves all knowledge bases accessible to the authenticated user. + + **Key Features:** + - Returns complete collection of knowledge bases + - Includes metadata and document lists + - Supports pagination (implied by array response) + + **Key Rules:** + - Requires `knowledge-base:knowledge-bases:read` scope + - Returns empty array if no knowledge bases exist + + **Response Characteristics:** + - **200 OK**: Array of `KnowledgeBase` objects + - **401 Unauthenticated**: Invalid/missing credentials + - **403 Forbidden**: Insufficient permissions + - **500 Internal Server Error**: Data retrieval failure + tags: + - Knowledge Base + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:knowledge-bases:read + responses: + '200': + description: List of knowledge bases + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + /knowledge-bases/{knowledgeBaseId}: + parameters: + - name: knowledgeBaseId + in: path + required: true + schema: + type: string + description: ID of the knowledge base + - $ref: '#/components/parameters/x-correlator' # Added correlator + + get: + operationId: getKnowledgeBase + summary: Get a specific knowledge base + description: | + Retrieves metadata and document list for a specific knowledge base. + + **Key Features:** + - Returns detailed metadata (name, description) + - Includes list of documents with filenames/formats + - Provides document upload timestamps + + **Key Rules:** + - Requires valid `knowledgeBaseId` path parameter + - Requires `knowledge-base:knowledge-bases:read` scope + + **Response Characteristics:** + - **200 OK**: Complete `KnowledgeBase` object + - **404 Not Found**: Invalid/non-existent knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Data retrieval failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:read + responses: + '200': + description: Knowledge base details + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + put: + operationId: updateKnowledgeBase + summary: Update a knowledge base + description: | + Updates metadata of an existing knowledge base. + + **Key Features:** + - Modifies name and/or description + - Preserves existing document associations + - Returns updated metadata + + **Key Rules:** + - Requires at least one update field (name/description) + - Requires `knowledge-base:knowledge-bases:update` scope + - knowledgeBaseId must exist + + **Response Characteristics:** + - **200 OK**: Updated `KnowledgeBase` object + - **400 Bad Request**: No update fields provided + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Update processing failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:update + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBaseUpdateRequest' + responses: + '200': + description: Knowledge base updated successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + delete: + operationId: deleteKnowledgeBase + summary: Delete a knowledge base + description: | + Permanently deletes a knowledge base and its documents. + + **Key Features:** + - Removes knowledge base metadata + - Deletes all associated documents + - Irreversible operation + + **Key Rules:** + - Requires valid `knowledgeBaseId` + - Requires `knowledge-base:knowledge-bases:delete` scope + - No partial deletions + + **Response Characteristics:** + - **204 No Content**: Successful deletion (no body) + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Deletion processing failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:delete + responses: + '204': + description: Knowledge base deleted successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + /knowledge-bases/{knowledgeBaseId}/documents: + post: + operationId: uploadDocument + summary: Upload a document to a knowledge base + description: | + Uploads a document to a knowledge base. + + **Key Features:** + - Supports doc/pdf/txt/csv formats + - Stores filename and format metadata + - Records upload timestamp + + **Key Rules:** + - Requires valid `knowledgeBaseId` + - Requires `knowledge-base:documents:update` scope + - File must be sent as multipart/form-data + - Maximum file size determined by implementation + + **Response Characteristics:** + - **201 Created**: Success message with filename + - **400 Bad Request**: Invalid file format + - **415 Unsupported Media Type**: Unacceptable format + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Storage failure + tags: + - Documents + parameters: + - name: knowledgeBaseId + in: path + required: true + schema: + type: string + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:documents:update + requestBody: + content: + multipart/form-data: + schema: + type: object + properties: + document: + type: string + format: binary + required: + - document + required: true + responses: + '201': + description: Document uploaded successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: object + properties: + message: + type: string + example: "Document uploaded successfully" + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '415': + $ref: '#/components/responses/Generic415' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for request tracing + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + KnowledgeBase: + type: object + properties: + knowledgeBaseId: + type: string + description: Unique identifier of the knowledge base + name: + type: string + description: Name of the knowledge base + description: + type: string + description: Detailed description of the knowledge base + documents: + type: array + items: + type: object + properties: + filename: + type: string + format: + type: string + enum: [doc, pdf, txt, csv] + description: File format + uploadDate: + type: string + format: date-time + description: "Upload timestamp. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ" + description: List of documents in the knowledge base + + KnowledgeBaseCreateRequest: + type: object + required: + - name + properties: + name: + type: string + description: Name of the knowledge base + description: + type: string + description: Detailed description of the knowledge base + + KnowledgeBaseUpdateRequest: + type: object + properties: + name: + type: string + description: New name of the knowledge base + description: + type: string + description: New description of the knowledge base + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_DOCUMENT_FORMAT + - MISSING_REQUIRED_PARAM + examples: + GENERIC_400_INVALID_DOCUMENT_FORMAT: + description: Invalid document format + value: + status: 400 + code: INVALID_DOCUMENT_FORMAT + message: "Invalid document format. Supported formats: doc/pdf/txt/csv" + GENERIC_400_MISSING_REQUIRED_PARAM: + description: Missing required parameter + value: + status: 400 + code: MISSING_REQUIRED_PARAM + message: "Required parameter 'name' is missing" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions for this operation + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - KNOWLEDGE_BASE_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_KNOWLEDGE_BASE_NOT_FOUND: + description: Knowledge base not found + value: + status: 404 + code: KNOWLEDGE_BASE_NOT_FOUND + message: "Specified knowledge base ID does not exist" + + Generic415: + description: Unsupported media type + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 415 + code: + enum: + - UNSUPPORTED_MEDIA_TYPE + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Unsupported document format + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: "Unsupported document format. Supported formats: doc/pdf/txt/csv" + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred" +``` diff --git a/marked/ModelAsAService/code/API_definitions/qa-assistant-manage/raw.md b/marked/ModelAsAService/code/API_definitions/qa-assistant-manage/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..05b4e1ebe9e2ff034ae59fbaf4b022fa4e4ca5c7 --- /dev/null +++ b/marked/ModelAsAService/code/API_definitions/qa-assistant-manage/raw.md @@ -0,0 +1,630 @@ +# qa-assistant-manage + +```yaml +openapi: 3.0.3 +info: + title: Q&A Assistant - Manage + description: >- + This API provides CRUD (Create, Read, Update, Delete) management functions for the Question and Answer (Q&A) Assistant, aiming to equip developers with the capability to configure and manage intelligent question-answering systems based on Large Language Models (LLMs). + It supports model parameter tuning, knowledge base association, and prompt engineering configuration, making it suitable for building customizable intelligent customer service or question-answering services. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scopes are required: + - qa-assistant-manage:assistants:create - Create new assistants + - qa-assistant-manage:assistants:read - Read assistant details + - qa-assistant-manage:assistants:update - Update existing assistants + - qa-assistant-manage:assistants:delete - Delete assistants + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/qa-assistant-manage/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /assistants: + post: + operationId: createAssistant + summary: Create a new QA assistant + description: | + Creates a new QA assistant configuration. + + **Key Features:** + - Configures LLM parameters (model, temperature, max_tokens) + - Associates with knowledge bases + - Sets behavior-defining prompts + + **Key Rules:** + - Requires `name`, `configurationPrompt`, and `largeModelParameters` + - `largeModelParameters` must include `model`, `temperature` (0.0-1.0), `max_tokens` (≥1) + - Needs `qa-assistant-manage:assistants:create` scope + + **Response Characteristics:** + - **201 Created**: Returns `AssistantResponse` with generated assistantId + - **400 Bad Request**: Missing parameters or invalid values (e.g., temperature out of range) + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Assistant creation failure + tags: + - Assistants + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-manage:assistants:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantCreateRequest' + responses: + '201': + description: Assistant created successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + get: + operationId: listAssistants + summary: List all QA assistants + description: | + Retrieves all configured QA assistants. + + **Key Features:** + - Returns complete assistant configurations + - Includes metadata (createdAt, updatedAt) + - Shows associated knowledge bases + + **Key Rules:** + - Requires `qa-assistant-manage:assistants:read` scope + - Returns empty array if no assistants exist + + **Response Characteristics:** + - **200 OK**: Array of `Assistant` objects + - **401 Unauthenticated**: Invalid credentials + - **403 Forbidden**: Insufficient permissions + - **500 Internal Server Error**: Data retrieval failure + tags: + - Assistants + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-manage:assistants:read + responses: + '200': + description: List of assistants + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/Assistant' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + /assistants/{assistantId}: + parameters: + - name: assistantId + in: path + required: true + schema: + type: string + description: Unique identifier of the assistant + - $ref: '#/components/parameters/x-correlator' # Added correlator + + get: + operationId: getAssistant + summary: Get a specific QA assistant + description: | + Retrieves detailed configuration for a specific assistant. + + **Key Features:** + - Returns full LLM parameter configuration + - Includes knowledge base associations + - Shows prompt configurations + + **Key Rules:** + - Requires valid UUID `assistantId` + - Needs ` knowledge-base:documents:update` scope + + **Response Characteristics:** + - **200 OK**: Complete `Assistant` object + - **404 Not Found**: Invalid/non-existent assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Configuration retrieval failure + tags: + - Assistants + security: + - openId: + - knowledge-base:documents:update + responses: + '200': + description: Assistant details + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/Assistant' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + put: + operationId: updateAssistant + summary: Update a QA assistant + description: | + Modifies an existing QA assistant configuration. + + **Key Features:** + - Updates LLM parameters dynamically + - Changes knowledge base associations + - Modifies behavior prompts + + **Key Rules:** + - Requires valid UUID `assistantId` + - At least one update field must be provided + - Parameter values must meet constraints (e.g., temperature 0.0-1.0) + - Needs `qa-assistant-manage:assistants:update` scope + + **Response Characteristics:** + - **200 OK**: Returns updated `AssistantResponse` + - **400 Bad Request**: Invalid parameters or no update fields + - **404 Not Found**: Invalid assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Update processing failure + tags: + - Assistants + security: + - openId: + - qa-assistant-manage:assistants:update + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantUpdateRequest' + responses: + '200': + description: Assistant updated successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + delete: + operationId: deleteAssistant + summary: Delete a QA assistant + description: | + Permanently removes a QA assistant configuration. + + **Key Features:** + - Irreversible deletion + - Cleans up associated resources + - Immediate deactivation + + **Key Rules:** + - Requires valid UUID `assistantId` + - Needs `qa-assistant-manage:assistants:delete` scope + - Cannot be undone + + **Response Characteristics:** + - **204 No Content**: Successful deletion (no body) + - **404 Not Found**: Invalid assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Deletion processing failure + tags: + - Assistants + security: + - openId: + - qa-assistant-manage:assistants:delete + responses: + '204': + description: Assistant deleted successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + AssistantCreateRequest: + type: object + required: + - name + - configurationPrompt + - largeModelParameters + properties: + name: + type: string + description: Name of the assistant + description: + type: string + description: Description of the assistant + knowledgeBaseId: + type: string + description: Optional ID of the associated knowledge base + configurationPrompt: + type: string + description: Configuration prompt for the assistant + largeModelParameters: + type: object + description: Parameters for the large language model + required: + - model + - parameters + properties: + model: + type: string + example: "gpt-4" + parameters: + type: object + required: + - temperature + - max_tokens + properties: + temperature: + type: number + format: float + minimum: 0.0 + maximum: 1.0 + example: 0.7 + max_tokens: + type: integer + minimum: 1 + example: 200 + top_p: + type: number + format: float + minimum: 0.0 + maximum: 1.0 + example: 0.8 + openingRemarks: + type: string + description: Optional opening remarks for the assistant + + AssistantUpdateRequest: + type: object + properties: + name: + type: string + description: New name of the assistant + description: + type: string + description: New description of the assistant + knowledgeBaseId: + type: string + description: Optional new knowledge base ID + configurationPrompt: + type: string + description: Updated configuration prompt + largeModelParameters: + type: object + description: Updated model parameters + properties: + model: + type: string + parameters: + type: object + properties: + temperature: + type: number + format: float + max_tokens: + type: integer + top_p: + type: number + format: float + openingRemarks: + type: string + description: Updated opening remarks + + Assistant: + type: object + properties: + assistantId: + type: string + description: Unique identifier of the assistant + format: uuid + example: "a1b2c3d4-5678-90ab-cdef-1234567890ab" + name: + type: string + description: + type: string + knowledgeBaseId: + type: string + configurationPrompt: + type: string + largeModelParameters: + type: object + properties: + model: + type: string + parameters: + type: object + openingRemarks: + type: string + createdAt: + type: string + format: date-time + updatedAt: + type: string + format: date-time + + AssistantResponse: + type: object + properties: + success: + type: boolean + description: Whether the operation succeeded + assistantId: + type: string + description: Unique identifier of the assistant + format: uuid + message: + type: string + description: Success/failure message + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - MISSING_REQUIRED_PARAM + - INVALID_PARAMETER_VALUE + - INVALID_ARGUMENT + examples: + GENERIC_400_MISSING_REQUIRED_PARAM: + description: Missing required parameter + value: + status: 400 + code: MISSING_REQUIRED_PARAM + message: "Required parameter 'configurationPrompt' is missing" + GENERIC_400_INVALID_PARAMETER_VALUE: + description: Invalid parameter value + value: + status: 400 + code: INVALID_PARAMETER_VALUE + message: "Temperature must be between 0.0 and 1.0" + GENERIC_400_INVALID_ARGUMENT: + description: Invalid argument + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions for this operation + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Token context inconsistency + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "Assistant ID is not consistent with access token" + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ASSISTANT_NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_ASSISTANT_NOT_FOUND: + description: Assistant not found + value: + status: 404 + code: ASSISTANT_NOT_FOUND + message: "Specified assistant ID does not exist" + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Assistant identifier not found. + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + - INTERNAL + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred" + GENERIC_500_INTERNAL: + description: Internal server error + value: + status: 500 + code: INTERNAL + message: Unknown server error +``` diff --git a/marked/ModelAsAService/code/API_definitions/qa-assistant-service/raw.md b/marked/ModelAsAService/code/API_definitions/qa-assistant-service/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..250bdd07c6dd1c9e3bb8cd18decb6c74e7f2e36f --- /dev/null +++ b/marked/ModelAsAService/code/API_definitions/qa-assistant-service/raw.md @@ -0,0 +1,367 @@ +# qa-assistant-service + +```yaml +openapi: 3.0.3 +info: + title: Q&A Assistant - Service + description: >- + This API provides service interfaces for the Question and Answer (Q&A) Assistant, enabling users to submit query requests to a configured Q&A assistant and obtain answers generated based on the knowledge base and Large Language Model (LLM). + It is suitable for scenarios such as building intelligent question-answering systems and customer service bots that require real-time responses to user inquiries. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scope is required: + - qa-assistant-service:answer:read - Permission to query assistants + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/qa-assistant-service/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /answer: + post: + operationId: queryAssistant + summary: Get an answer from a QA assistant + description: | + Queries a configured QA assistant to generate answers using knowledge bases and LLMs. + + **Key Features:** + - Utilizes pre-configured assistant settings (prompts, model parameters) + - Leverages associated knowledge bases for contextual responses + - Provides termination status for answer generation + + **Key Rules:** + - Requires valid UUID `assistantId` + - `prompt` must be 1-1000 characters + - Needs `qa-assistant-service:answer:read` scope + - Assistant must be properly configured and accessible + + **Response Characteristics:** + - **200 OK**: Returns `QueryResponse` with answer text and termination status + - `finished` indicates generation completion reason (Stop/Length/Error/Filter) + - `reference` shows knowledge base source when available + - **400 Bad Request**: + - Missing/invalid prompt + - Invalid assistantId format + - Prompt length exceeds limits + - **401 Unauthenticated**: Missing/invalid credentials + - **403 Forbidden**: + - Missing required scope + - Token/assistantId mismatch + - **404 Not Found**: + - Assistant doesn't exist + - Identifier not found + - **500 Internal Server Error**: + - LLM processing failure + - Knowledge base access error + tags: + - Query + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-service:answer:read + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/QueryRequest' + responses: + '200': + description: Successful answer retrieval + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/QueryResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for request tracing + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + QueryRequest: + type: object + required: + - assistantId + - prompt + properties: + assistantId: + type: string + format: uuid + description: Unique identifier of the QA assistant + example: "a1b2c3d4-5678-90ab-cdef-1234567890ab" + prompt: + type: string + minLength: 1 + maxLength: 1000 + description: The user's question or query + example: "How do I reset my password?" + + QueryResponse: + type: object + required: + - success + - finished + - answerText + properties: + success: + type: boolean + description: Indicates whether the query was processed successfully + finished: + type: string + description: Termination status of the response generation + enum: + - Stop + - Length + - Error + - Filter + example: "Stop" + answerText: + type: string + description: The assistant's generated answer + example: "To reset your password, go to settings > security..." + reference: + type: string + description: Optional reference to the knowledge base source + example: "kb123_section5" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - MISSING_PROMPT + - INVALID_ASSISTANT_ID + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_MISSING_PROMPT: + description: Missing required prompt parameter + value: + status: 400 + code: MISSING_PROMPT + message: "Required parameter 'prompt' is missing" + GENERIC_400_INVALID_ASSISTANT_ID: + description: Invalid assistant ID format + value: + status: 400 + code: INVALID_ASSISTANT_ID + message: "Assistant ID must be a valid UUID" + GENERIC_400_INVALID_ARGUMENT: + description: Invalid argument + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument" + GENERIC_400_OUT_OF_RANGE: + description: Parameter value out of range + value: + status: 400 + code: OUT_OF_RANGE + message: "Prompt length exceeds maximum allowed characters" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions to query this assistant + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Token context inconsistency + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "Assistant ID is not consistent with access token" + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ASSISTANT_NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_ASSISTANT_NOT_FOUND: + description: Assistant not found + value: + status: 404 + code: ASSISTANT_NOT_FOUND + message: "Specified assistant ID does not exist" + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Assistant identifier not found. + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + - INTERNAL + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred while processing query" + GENERIC_500_INTERNAL: + description: Internal server error + value: + status: 500 + code: INTERNAL + message: Unknown server error +``` diff --git a/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story/raw.md b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9f6a902cc353dd94c0bd8220c00a5b75bd0604b7 --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story/raw.md @@ -0,0 +1,10 @@ +# Model as a Service - Knowledge Base User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a standardized API to create, manage, and populate knowledge bases with documents, so that I can build knowledge-intensive applications (like intelligent customer service or enterprise wikis) with fine-grained access control and full traceability. | +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server)
            **Actors:** Application Service Provider, End-Users interacting with the knowledge-based application.
            **Scope:** Full CRUD (Create, Read, Update, Delete) lifecycle management of knowledge base resources and document upload.| +| ***Pre-conditions*** |
            • The API Consumer (application server) is onboarded to the CSP's API platform.
            • The API Consumer has successfully subscribed to the Knowledge Base API product.
            • The API Consumer has obtained a valid OAuth 2.0 access token with the required scopes for the intended operation (e.g., knowledge-base:knowledge-bases:create).
            | +| ***Activities/Steps*** |Starts when: The API Consumer application server makes an authenticated API request (e.g., POST /knowledge-bases to create a new knowledge base).
            Ends when: The requested operation is completed by the API server and a success or error response is received (e.g., 201 Created for a successful creation). | +| ***Post-conditions*** |The state of the knowledge base system is changed according to the operation (e.g., a new knowledge base is created and available, a document is added to a knowledge base, a knowledge base is deleted). The API consumer can proceed with its application logic. | +| ***Exceptions*** |
            • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope.
            • 400 Bad Request: Invalid input (e.g., missing required 'name' field, invalid document format).
            • 404 Not Found: Referenced resource (e.g., knowledgeBaseId) does not exist.
            • 415 Unsupported Media Type: Attempting to upload a document type not supported (e.g., not doc, pdf, txt, csv).
            • 500 Internal Server Error: An unexpected error occurred on the server during processing.
            | diff --git a/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story/raw.md b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6b9ed6bd73c0ebbf669a279711016a4c68f592b6 --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story/raw.md @@ -0,0 +1,10 @@ +# Model as a Service - Knowledge Base and Q&A Assistant User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application development lead at a financial services company, I need to leverage a comprehensive set of knowledge management and intelligent Q&A APIs to transform our extensive financial product documentation, compliance guidelines, and customer service manuals into a smart Q&A system. This will enable our clients to quickly obtain accurate product information and compliance advice through natural language queries, while our customer service team can handle complex inquiries more efficiently. Ultimately, this will enhance customer satisfaction and reduce operational costs.| +| ***Roles, Actor(s) and scope*** |**Actors:**
            • Financial Services Company:Development Lead - Decides on API integration and leads the development team
            • Financial Services Company:Development Team - Implements API integration
            • Financial Services Company:Customer Service Manager - Defines knowledge base content and Q&A requirements
            • Financial Services Company:Compliance Officer - Ensures content meets regulatory requirements
            • End Customer - End-user utilizing the intelligent Q&A functionality
            • Customer Service Representative - Uses the system to assist customer service
            • Communication Service Provider (CSP) - Provides the API platform and services

            **Scope:**
            • Creation and management of multiple knowledge bases (e.g., "Investment Products," "Loan Services," "Compliance Guidelines")
            • Upload of documents in various formats (PDF product brochures, DOCX compliance documents, TXT FAQs, CSV data sheets)
            • Configuration of dedicated Q&A assistants for different scenarios (e.g., "Investment Advisor Assistant," "Loan Specialist Assistant")
            • Adjustment of large language model parameters to optimize answer quality and style
            • API queries to obtain intelligent answers based on the knowledge base
            • Tracking answer sources to ensure compliance and auditability| +| ***Pre-conditions*** |The following prerequisites must be met:
            1. Financial Services Company:Development Lead has evaluated and selected the CSP's API solution, and Customer Service Manager and Compliance Officer have confirmed requirements
            2. The company has subscribed to the Knowledge Base and Q&A Assistant API product package through the CSP's business portal
            3. Development Team has registered the company application on the CSP platform and obtained necessary credentials (e.g., client ID and secret)
            4. The company backend system has implemented the OAuth 2.0 client flow and can obtain access tokens with required scopes (e.g., knowledge-base:knowledge-bases:create, qa-assistant-service:answer:read)
            5. Compliance Officer has reviewed and approved the data processing plan to ensure compliance with financial industry regulations (e.g., GDPR, PCI DSS)| +| ***Activities/Steps*** |**Starts when:** The company decides to implement an intelligent Q&A system to improve customer service quality

            **Typical implementation and usage process:**
            1. Knowledge Base Planning - Customer Service Manager and Compliance Officer jointly determine the scope and categorization of documents to be digitized
            2. Knowledge Base Creation - Development Team calls POST /knowledge-bases to create structured knowledge bases like "Investment Products" and "Loan Services"
            3. Document Upload - Use POST /knowledge-bases/{id}/documents to batch upload documents such as product brochures and compliance files
            4. Assistant Configuration - Create Q&A assistants for different scenarios via POST /assistants, setting specialized configurationPrompt to ensure answers comply with financial industry standards
            5. Model Tuning - Adjust largeModelParameters such as temperature and max_tokens based on Customer Service Manager feedback to balance answer creativity and accuracy
            6. System Integration - Integrate the Q&A API (POST /answer) into the company website, mobile apps, and customer service workstation
            7. Customer Query - End Customer asks questions through company channels, and the system uses the appropriate assistantId and user question as prompt to call the API
            8. Answer Generation - CSP service returns a response containing answerText and reference, ensuring answers are traceable to knowledge base sources
            9. Continuous Optimization - Regularly update knowledge base content and assistant configurations based on user feedback and customer service usage

            **Ends when:** The customer receives accurate, helpful answers, and all interactions comply with regulatory requirements| +| ***Post-conditions*** |• The company maintains a continuously updated digital knowledge base containing all important financial product and compliance documentation
            • Multiple dedicated Q&A assistants are configured and capable of handling customer queries across different domains
            • Customers can quickly obtain accurate financial information through natural language without navigating complex documents
            • Customer service representatives can use the system to quickly respond to complex inquiries, improving work efficiency
            • All Q&A interactions are recorded and traceable to sources, meeting financial industry compliance and audit requirements
            • The system can be easily expanded as business grows, adding new knowledge bases and assistants| +| ***Exceptions*** |Potential exceptions and handling methods:

            • 401 Unauthorized/403 Forbidden - Invalid access token or insufficient permissions (e.g., attempting to upload documents with read-only token). The system should reacquire a valid token or prompt the administrator to adjust permissions
            • 400 Bad Request - Input parameters do not meet requirements (e.g., missing knowledge base name, prompt exceeding 1000 characters, temperature parameter outside 0.0-1.0 range). Should validate inputs and provide clear error messages
            • 404 Not Found - Requested resource does not exist (e.g., using incorrect knowledge base ID or assistant ID). Should verify the correctness of resource identifiers
            • 415 Unsupported Media Type - Attempting to upload unsupported file formats. Should restrict upload file types and validate in advance
            • 500 Internal Server Error - Server-side processing error (e.g., LLM processing failure, document parsing error). Should log error details and implement retry mechanisms, while notifying administrators
            • Insufficient Answer Quality - Generated answers are inaccurate or incomplete. Should optimize by improving prompt engineering, adjusting model parameters, or enhancing knowledge base content
            • Response Delay - Q&A response time is too long, affecting user experience. Should consider implementing asynchronous processing or caching common answers
            • Compliance Risks - Answer content may involve compliance issues. Should establish manual review processes and content filtering mechanisms to ensure compliance with financial regulations| diff --git a/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story/raw.md b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bd2d0d32593809ec59aea48c8578a7052514e9b0 --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story/raw.md @@ -0,0 +1,10 @@ +# Model as a Service - Q&A Assistant Manage User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a standardized API to create, configure, and manage intelligent Q&A assistants based on Large Language Models (LLMs), so that I can build customizable intelligent customer service or question-answering systems with fine-grained control over model behavior, knowledge sources, and prompting strategies. | +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server)
            **Actors:** Application Service Provider, End-Users interacting with the Q&A service.
            **Scope:** Full CRUD (Create, Read, Update, Delete) lifecycle management of Q&A assistant configurations, including LLM parameter tuning, knowledge base association, and prompt engineering.| +| ***Pre-conditions*** |
            • The API Consumer (application server) is onboarded to the CSP's API platform.
            • The API Consumer has successfully subscribed to the Q&A Assistant Management API product.
            • The API Consumer has obtained a valid OAuth 2.0 access token with the required scopes for the intended operation (e.g., qa-assistant-manage:assistants:create).
            | +| ***Activities/Steps*** |**Starts when:** The API Consumer application server makes an authenticated API request (e.g., POST /assistants to create a new assistant with specified LLM parameters and prompts).
            **Ends when:** The requested operation is completed by the API server and a success or error response is received (e.g., 201 Created with a generated assistantId).| +| ***Post-conditions*** |The state of the Q&A assistant system is changed according to the operation (e.g., a new assistant configuration is created and available, an existing assistant's parameters are updated). The API consumer can use the configured assistant for intelligent question-answering.| +| ***Exceptions*** |
            • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope; token context inconsistency.
            • 400 Bad Request: Invalid input (e.g., missing required parameters like name or configurationPrompt, parameter values like temperature outside allowed range 0.0-1.0).
            • 404 Not Found: Referenced resource (e.g., assistantId) does not exist.
            • 500 Internal Server Error: An unexpected error occurred on the server during processing (e.g., assistant creation or update failure).
            | diff --git a/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story/raw.md b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..147d5a8627f2676340386e4e814ebfbae6ad1cce --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story/raw.md @@ -0,0 +1,10 @@ +# Model as a Service - Q&A Assistant Service User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a service API to submit user queries to a pre-configured Q&A assistant, so that I can integrate intelligent, knowledge-based question-answering capabilities into my applications, providing real-time responses to end-user inquiries through LLM-powered assistants.| +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server), End-User
            **Actors:** Application Service Provider, End-Users submitting queries.
            **Scope:** Submitting query requests to configured assistants and retrieving generated answers based on knowledge bases and LLM configurations.| +| ***Pre-conditions*** |
            • The API Consumer (application server) is onboarded to the CSP's API platform.
            • The API Consumer has successfully subscribed to the Q&A Assistant Service API product.
            • A Q&A assistant has been previously configured and is accessible via its assistantId.
            • The API Consumer has obtained a valid OAuth 2.0 access token with the required qa-assistant-service:answer:read scope.
            | +| ***Activities/Steps*** |**Starts when:** The API Consumer application server makes an authenticated POST request to /answer with a valid assistantId and a user prompt (1-1000 characters).
            **Ends when:** The API server processes the query using the configured assistant and knowledge base, then returns a response containing the generated answer and termination status.| +| ***Post-conditions*** |The end-user receives an intelligent response to their query. The API response includes the generated answer text, completion status (finished field indicating Stop/Length/Error/Filter), and optional knowledge base reference. The application can display this answer to the user.| +| ***Exceptions*** |
            • 400 Bad Request: Missing or invalid parameters (e.g., missing prompt, invalid UUID format for assistantId, prompt length exceeds 1000 characters).
            • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope; token/assistantId context mismatch.
            • 404 Not Found: The specified assistantId does not exist or is not accessible.
            • 500 Internal Server Error: Backend processing failure (e.g., LLM processing error, knowledge base access issue).
            | diff --git a/marked/ModelAsAService/documentation/API_documentation/README/raw.md b/marked/ModelAsAService/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist/raw.md b/marked/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5baaebc38964f0b0d7bdbb24c701c3814b49945a --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for knowledge-base v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [knowledge-base.yaml](/code/API_definitions/knowledge-base.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md),| +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/marked/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist/raw.md b/marked/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..32d9cfb82e4b8b95ef1b52f39ac57c905f8afaef --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qa-assistant-manage v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qa-assistant-manage.yaml](/code/API_definitions/qa-assistant-manage.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md)| +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/marked/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist/raw.md b/marked/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..920e83f727b8afa2f8c5f54b576d4fc28dd39899 --- /dev/null +++ b/marked/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qa-assistant-service v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qa-assistant-service.yaml](/code/API_definitions/qa-assistant-service.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/marked/ModelAsAService/documentation/SupportingDocuments/README/raw.md b/marked/ModelAsAService/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ModelAsAService/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/MostFrequentLocation/README/raw.md b/marked/MostFrequentLocation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b89599661cce69ff4abf5712b15a404bd0bc6dd7 --- /dev/null +++ b/marked/MostFrequentLocation/README/raw.md @@ -0,0 +1,54 @@ + + + + + + + + + +# MostFrequentLocation + +Sandbox API Repository to describe, develop, document, and test the MostFrequentLocation Service API(s). The repository does not yet belong to a CAMARA Sub Project, but works together with DeviceVisitLocation as Location Insights. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XjPe) + +## Scope + +* Service APIs for “MostFrequentLocation” (see APIBacklog.md) +* It provides the API Consumer with the ability to: + * "MostFrequentLocation": validate, in terms of scoring, of the user's expected home area + * NOTE: The scope of these APIs should be limited (at least at the first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/MostFrequentLocation/releases/tag/r2.2) (Fall25), with the following API versions: + * **most-frequent-location v0.2.0** + [[YAML]](https://github.com/camaraproject/MostFrequentLocation/blob/r2.2/code/API_definitions/most-frequent-location.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/MostFrequentLocation/r2.2/code/API_definitions/most-frequent-location.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/MostFrequentLocation/r2.2/code/API_definitions/most-frequent-location.yaml) +* The latest public release is always available here: https://github.com/camaraproject/MostFrequentLocation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/MostFrequentLocation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/MostFrequentLocation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: On-demand + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99479758031?password=c705dd6f-a1c5-44e4-af97-331a18395fb8) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564467/MostFrequentLocation+2024+Minutes) + * Slack channel: [camara-project.slack.com](https://camara-project.slack.com/archives/C07BHCZ3XUY) #sp-location-insights +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/MostFrequentLocation/code/API_definitions/most-frequent-location/raw.md b/marked/MostFrequentLocation/code/API_definitions/most-frequent-location/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..327cdf559ccfb8e881f7176e568e00fd7b1a79c3 --- /dev/null +++ b/marked/MostFrequentLocation/code/API_definitions/most-frequent-location/raw.md @@ -0,0 +1,590 @@ +# most-frequent-location + +```yaml +openapi: 3.0.3 +info: + title: Most Frequent Location + description: | + The Most Frequent Location API provides API Consumers with the ability to verify the frequency of a device's location within a specific geographic area. + + # Introduction + + This API verifies if a device is present most of the time in a certain location. This location insight is useful as an approach to the residence location of the end-user. + + This API can be used in anti-fraud cases where an application provider needs further evidence about the reported place of residence of the end-user. Also, for service provision or personalization tasks when the service provider needs to manage their offer depending on the habits of the end-user. + + Such use cases are transversal to different sectors such as: + + - Financial institutions: to mitigate risks about identity fraud, helping in their compliance with AML/KYC regulation. + - Insurance companies: to assess risks and prevent fraudulent claims. + - E-commerce and retail: to ensure accurate shipping and delivery, fraud prevention and targeted marketing. + - Digital Content Delivery companies: to verify service provisioning and billing, and to comply with regulation. + - Utilities: to verify service provisioning and billing, and to prevent service theft. + - Real estate: to screen potential tenants and ensure that lease agreements are in compliance with local laws. + + # Relevant terms and definitions + + * **Device**: End-user equipment able to connect to a network. Examples of devices include smartphones, home gateways or IoT sensors/actuators. + + * **Geographical reference**: Using coordinates or a reference code, the geographical surface where a device can be physically located is specified. + + * **Verification**: The process triggered on the API server to calculate the frequency of time a device is at a given location. + + # API functionality + + The API allows API Consumers to verify the frequency with which a device is in a specific location. The location can be specified using a geographical reference of type: + - `COVERAGE_ZONE`: It is specified by latitude and longitude coordinates. The coverage area is generated by one or more antennas closest to the specified coordinates, determining the device's connection to these antennas. + - `POSTAL_CODE`: A zip code or postal code that delimits a geographic area. + + The operation returns a score representing how frequently the device was connected to antennas whose coverage cover the requested area in certain time slots. The range of score values is between "0" and "100", where higher scores indicate a more frequent presence in the location. + + The `score` value maps to the frequency as follows: + - `score = 0`: The device has never been in the specified location. + - `score = 100`: The device is almost always in the specified location. + + ## Identifying a device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.2.0 + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/MostFrequentLocation +servers: + - url: "{apiRoot}/most-frequent-location/v0.2" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Frequent location verification + description: Verification of the most frequent location of a device +paths: + /verify: + post: + security: + - openId: + - most-frequent-location:verify + tags: + - Frequent location verification + summary: Verify the most frequent location of a device + description: |- + Verify the frequency with which a device is within a requested geographic area location. The location can be defined by a postal code or a latitude and longitude coordinates. The operation returns a score representing how frequently the device was connected to antennas whose coverage covers the requested area. + operationId: verifyFrequentLocation + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Request body with a device as identifier and geographical reference for location + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyFrequentLocationRequest' + examples: + INPUT_PHONE_NUMBER_POSTAL_CODE: + summary: Phone number and postal code + description: Verify the frequency with which the device, identified by a phone number, has been in a location delimited by a postal code + value: + device: + phoneNumber: '+123456789' + geoReference: + type: POSTAL_CODE + postalCode: '12345' + INPUT_PHONE_NUMBER_COVERAGE_ZONE: + summary: Phone number and coverage zone + description: Verify the frequency with which the device, identified by a phone number, has been in a location delimited by a coverage zone specified by latitude and longitude coordinates + value: + device: + phoneNumber: '+123456789' + geoReference: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + INPUT_IP_ADDRESS_V4_POSTAL_CODE: + summary: IPv4 address and postal code + description: Verify the frequency with which the device, identified by an IPv4 address, has been in a location delimited by a postal code + value: + device: + ipv4Address: + publicAddress: '123.234.1.2' + publicPort: 1234 + geoReference: + type: POSTAL_CODE + postalCode: '12345' + INPUT_IP_ADDRESS_V4_COVERAGE_ZONE: + summary: IPv4 address and coverage zone + description: Verify the frequency with which the device, identified by an IPv4 address, has been in a location delimited by a coverage zone specified by latitude and longitude coordinates + value: + device: + ipv4Address: + publicAddress: '123.234.1.2' + publicPort: 1234 + geoReference: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + responses: + '200': + description: Most frequent location verification result + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyFrequentLocationResponse' + examples: + HIGH_SCORE: + summary: High score with detail + description: The device has been at the requested location with high frequency for most of the time. + value: + score: 86 + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/VerifyFrequentLocationBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/VerifyFrequentLocationPermissionDenied403' + '404': + $ref: '#/components/responses/VerifyFrequentLocationNotFound404' + '422': + $ref: '#/components/responses/VerifyFrequentLocationUnprocessableEntity422' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + schemas: + VerifyFrequentLocationRequest: + type: object + description: Request with a device as identifier and geographical reference for location + required: + - geoReference + properties: + device: + $ref: '#/components/schemas/Device' + geoReference: + $ref: '#/components/schemas/GeoReference' + VerifyFrequentLocationResponse: + type: object + description: Calculated Score Response + required: + - score + properties: + score: + $ref: '#/components/schemas/Score' + Device: + description: |- + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + networkAccessIdentifier: + $ref: '#/components/schemas/NetworkAccessIdentifier' + ipv4Address: + $ref: '#/components/schemas/DeviceIpv4Addr' + ipv6Address: + $ref: '#/components/schemas/DeviceIpv6Address' + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access + identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: 123456789@domain.com + DeviceIpv4Addr: + type: object + description: |- + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: '#/components/schemas/SingleIpv4Addr' + privateAddress: + $ref: '#/components/schemas/SingleIpv4Addr' + publicPort: + $ref: '#/components/schemas/Port' + anyOf: + - required: + - publicAddress + - privateAddress + - required: + - publicAddress + - publicPort + example: + publicAddress: 84.125.93.10 + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: 84.125.93.10 + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: |- + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + GeoReference: + description: |- + Specific Geographical reference. It can be defined in different ways, such as by a postal code or coverage zone specified by latitude and longitude coordinates. + type: object + properties: + type: + $ref: '#/components/schemas/GeoReferenceType' + required: + - type + discriminator: + propertyName: type + mapping: + COVERAGE_ZONE: '#/components/schemas/CoverageZone' + POSTAL_CODE: '#/components/schemas/PostalCode' + GeoReferenceType: + type: string + description: |- + Type of this geographical reference. + - `COVERAGE_ZONE`: It is specified by latitude and longitude coordinates. The coverage area is generated by one or more antennas closest to the specified coordinates, determining the device's connection to these antennas. + - `POSTAL_CODE`: A zip code or postal code that delimits a geographic area. + enum: + - COVERAGE_ZONE + - POSTAL_CODE + CoverageZone: + description: Coverage zone specified by latitude and longitude coordinates + allOf: + - $ref: '#/components/schemas/GeoReference' + - type: object + properties: + latitude: + $ref: '#/components/schemas/Latitude' + longitude: + $ref: '#/components/schemas/Longitude' + example: + latitude: 50.735851 + longitude: 7.10066 + required: + - latitude + - longitude + example: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + PostalCode: + description: Area associated to an administrative or geographical code + allOf: + - $ref: '#/components/schemas/GeoReference' + - type: object + properties: + postalCode: + type: string + description: Zip code or postal code. + required: + - postalCode + Score: + type: integer + description: |- + The value is a summary metric derived from analysis of the device's connections to antennas covering the requested area across all time slots. + The range of score values is between "0" and "100", where higher scores indicate a more frequent presence in the location. + minimum: 0 + maximum: 100 + example: 86 + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represent + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + responses: + VerifyFrequentLocationBadRequest400: + description: |- + Bad Request. + In addition to regular scenario of `INVALID_ARGUMENT`, other scenarios may exist: + + - Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested ("code": "OUT_OF_RANGE","message": "Client specified an invalid range.") + - The postal code value does not exist or is invalid ("code": "MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID","message": "Requested postal code value does not exist or is invalid."). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + POSTAL_CODE_NOT_VALID: + description: The postal code value does not exist or is invalid + value: + status: 400 + code: MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID + message: Requested postal code value does not exist or is invalid. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + VerifyFrequentLocationPermissionDenied403: + description: |- + Forbidden. + In addition to regular scenario of `PERMISSION_DENIED`, another scenarios may exist: + + - Phone number cannot be deducted from access token context.("code": "INVALID_TOKEN_CONTEXT","message": "Phone number is not consistent with access token.") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + VerifyFrequentLocationNotFound404: + description: |- + Not found. + In addition to regular scenario of `NOT_FOUND`, other scenarios may exist: + + - Device identifier not found ("code": "IDENTIFIER_NOT_FOUND","message": "Device identifier not found."). + - There is not enough information to calculate the score ("code": "MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE","message": "Requested information is not available"). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + - MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + INFORMATION_NOT_AVAILABLE: + description: There is not enough information to calculate the score + value: + status: 404 + code: MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE + message: Requested information is not available. + VerifyFrequentLocationUnprocessableEntity422: + description: |- + Unprocessable Content. + + - Service is not available for the provided device ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided device."). + - None of the provided device identifiers are supported by the implementation ("code": "UNSUPPORTED_IDENTIFIER","message": "Supported device identifiers are: ..."). + - The device identifier is not included in the request and the device information cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The device cannot be identified."). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" +``` diff --git a/marked/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist/raw.md b/marked/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..24f18c55a060c0d429b4428a28de1ae16c0555f2 --- /dev/null +++ b/marked/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for most-frequent-location v0.2.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | public-release
            initial | public-release
            stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/most-frequent-location.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/most-frequent-location.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/most-frequent-location-check.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/most-frequent-location-check.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/G4LVB) | + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/marked/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations/raw.md b/marked/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..572f776c324ce8a22d662a919229a444d4abb31a --- /dev/null +++ b/marked/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations/raw.md @@ -0,0 +1,30 @@ +# Most Frequent Location API + +## Considerations about 'postalCode' and Country Name + +This document consolidates the discussion of the issue https://github.com/camaraproject/MostFrequentLocation/issues/7 + +### Problem description +Postal code is not globally unique. For example, 31000 is Pamplona in Spain and Toulouse in France. In most cases the country can be derived from the phone number, but there can be other more sophisticated cases. +Making postal code unique should help to detect error API calls. + +### Assumptions to solve and simplify the problem + +**Actors**: Application service provider (ASP), ASP:User, End-User, Communication Service Provider (CSP). + +**Assumptions**: +1. The End-User has a valid contract with a CSP in a specific country. +2. The CSP calculates the most frequent location insight of an End-User for that country where the CSP provides the service to the End-User. +3. The CSP can't provide the most frequent location insight for a country different from that of the contract. +4. The Application Service Provider User (ASP:User) wants to verify the most frequent location of the End-User using the 'phoneNumber' parameter of the API, which includes the country prefix. +6. The ASP:User assumes that the most frequent location insight is calculated for the country referred by the country prefix of the MSISDN. + +**Under these assumptions, the MFL API will return the insight expected by the ASP:User, and no additional parameter, such as 'countryName' is needed.** + +Any usage of the API out of these assumptions could provide misleading responses. For example, corner cases related with roaming, federation, or even coincident postal codes. + +## Other considerations + +If a common definition related to 'postalCode' is eventually specified at https://github.com/camaraproject/Commonalities, it will be reviewed for the evolution of this API. + +The only related issue so far does not consider 'postalCode': https://github.com/camaraproject/Commonalities/pull/315 \ No newline at end of file diff --git a/marked/MultiPointVPN/README/raw.md b/marked/MultiPointVPN/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17cacc85907c822891e7e432392201742f5f40e0 --- /dev/null +++ b/marked/MultiPointVPN/README/raw.md @@ -0,0 +1,41 @@ + + + + + + + + + +# MultiPointVPN + +Sandbox API Repository to describe, develop, document, and test the MultiPointVPN Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYD7Bw) + +## Scope + +* Service API(s) “MultiPointVPN” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * The MultiPoint VPN API transforms the process of ordering private or customized network services across multiple touchpoints. It enables users to create and configure on-demand edge connectivity services with guaranteed SLA and bandwidth with just one click, eliminating the need for manual orders through phone calls or customer managers. When the API is called with specific network SLA requirements, telecom operators can create non-public cloud leased network services by orchestrating IP VPN connections across various networks, including data centers, private clouds, operator networks, and satellite links +* Describe, develop, document, and test the API(s) +* Started: June 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly meeting on Wednesday every 2 week(s), at 12:30 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/AYD7Bw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/MultiPointVPN/code/API_definitions/README/raw.md b/marked/MultiPointVPN/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/MultiPointVPN/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/MultiPointVPN/code/API_definitions/multi-point-vpn/raw.md b/marked/MultiPointVPN/code/API_definitions/multi-point-vpn/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7f304f04306cfc9eac6363da222c9fc63e1041a5 --- /dev/null +++ b/marked/MultiPointVPN/code/API_definitions/multi-point-vpn/raw.md @@ -0,0 +1,638 @@ +# multi-point-vpn + +```yaml +openapi: 3.0.3 +info: + title: MultiPoint Virtual Private Network + description: > + ##### Before starting to use the API, the developer needs to know about the + below specified details : + + * Multipoint VPN service endpoint The URL pointing to the RESTful resource of the Multipoint VPN API. + + * Authentication Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the Multipoint VPN API. + + * Identifier for access point Customer Edge (CE) IPv4 addressand/or IPv6 address of the Customer Edge Router. + + * Identifier for the endpoint cloud Provider Edge (PE) IPv4 and/or IPv6 address of the Cloud Provider Edge. + + * Identifier for the application server(AS)IPv4 and/or IPv6 address of the application server (cloud virtual machine). + + * App-Flow (between the application client and application server). The developer wants to have non public network delivery for the precise application data flow for the application users. + + * Duration Duration (in hours) for which the Multipoint VPN session (between CE and cloud PE) should be created. This parameter is optional. + When not specified, a default session duration (e.g. 6 months) is applied. The user may request a termination before its expiration. + + * Physical Location Physical location of the Customer Edge Router. + + NOTE- The private physical link between CE and cloud PE is default deployed for one click calling, + otherwise it is required to install the physical link, which is out of the scope of this API. + version: wip + license: + name: Apache 2.0 + url: 'https://www.apache.org/licenses/LICENSE-2.0.html' + x-camara-commonalities: 0.5 +externalDocs: + description: Project documentation at CAMARA + url: 'https://github.com/camaraproject/MultiPointVPN' +servers: + - url: '{apiRoot}/multipointvpn/vwip' + variables: + apiRoot: + default: 'http://localhost:9091' + description: API root +tags: + - name: Network Assessment + description: Operations to manage Multipoint VPN connection assessments + - name: Network + description: Operations to manage Multipoint VPN connection +paths: + /network: + post: + tags: + - Network + summary: To create a multipoint virtual private network + description: Create a multipoint virtual private network + operationId: createNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkCreate" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionRequest" + responses: + "201": + description: CreateVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + /network/{serviceId}: + patch: + tags: + - Network + summary: To update a multipoint virtual private network + description: Update a new multipoint virtual private network + operationId: updateNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkUpdate" + examples: + SITE_TO_CLOUD_VPN_UPDATE_CONNECTION: + $ref: "#/components/examples/siteToCloudVPNUpdateConnectionRequest" + responses: + "200": + description: UpdateVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + get: + tags: + - Network + summary: retrieve multipoint virtual private network details + description: Retrieve multipoint virtual private network details + operationId: getVPNConnect + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + responses: + "200": + description: getNetworkDetails + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + delete: + tags: + - Network + summary: Delete multipoint virtual private network + description: Delete multipoint virtual private network + operationId: deleteNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + responses: + "202": + description: deleteVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + /assessment: + post: + tags: + - Network Assessment + summary: Assess Multipoint VPN connection feasibility + description: Get the feasibility assessment for a Multipoint VPN connection + operationId: assessConnectionFeasibility + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/AssessmentRequest" + examples: + SITE_TO_CLOUD_VPN_ASSESSMENT: + $ref: "#/components/examples/siteToCloudVPNFeasibilityAssessmentRequest" + responses: + "200": + description: Assessment result + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssessmentResult" + examples: + SITE_TO_CLOUD_VPN_ASSESSMENT_RESULT: + $ref: "#/components/examples/siteToCloudVPNFeasibilityAssessmentResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + serviceId: + name: serviceId + required: true + schema: + type: string + in: path + description: Identifier of the Resource + schemas: + Amount: + type: object + description: An amount in a given unit + properties: + amount: + type: number + format: float + default: 1 + description: Numeric value in a given unit + currency: + type: string + description: currency + AssessmentRequest: + description: Base schema for all areas + type: object + properties: + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + $ref: '#/components/schemas/Duration' + AssessmentResult: + type: object + properties: + waitdays: + type: integer + description: the waiting-days until the vpn can be offered + minimum: 1 + sla: + type: string + enum: + - A + - AA + - AAA + rent: + $ref: '#/components/schemas/Amount' + Connection: + allOf: + - type: object + description: Another Characteristic that is related to the current Characteristic; + properties: + id: + type: string + description: Unique identifier for the connection + customerEdge: + $ref: '#/components/schemas/EdgeConnection' + providerEdge: + $ref: '#/components/schemas/EdgeConnection' + Duration: + type: object + description: Guarantee duration + properties: + value: + type: number + format: float + default: 1 + description: Numeric value in a given unit + unit: + type: string + description: unit + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + EdgeConnection: + description: Edge connection details + type: object + properties: + type: + description: Multipoint VPN access point type + enum: + - site + - cloud + primaryIpAddress: + $ref: '#/components/schemas/IpAddress' + secondaryIpAddress: + $ref: '#/components/schemas/IpAddress' + location: + type: string + description: connection location + IpAddress: + type: object + properties: + addressType: + type: string + required: + - addressType + discriminator: + propertyName: addressType + mappings: + - Ipv4Addr: '#/components/schemas/Ipv4Address' + - Ipv6Addr: '#/components/schemas/Ipv6Address' + Ipv4Address: + allOf: + - $ref: '#/components/schemas/IpAddress' + - type: object + required: + - address + properties: + address: + type: string + format: ipv4 + Ipv6Address: + allOf: + - $ref: '#/components/schemas/IpAddress' + - type: object + required: + - address + properties: + address: + type: string + format: ipv6 + Network: + description: Base Network Entity structure + type: object + properties: + serviceId: + type: string + description: unique id for network service + serviceName: + type: string + description: vpn service name + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + sla: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + $ref: '#/components/schemas/Duration' + routeProtocal: + type: string + resourceGroupId: + type: string + cloudGatewayIP: + type: string + NetworkCreate: + description: Base Connection Entity structure + type: object + properties: + serviceName: + type: string + description: vpn service name + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + sla: + type: string + enum: + - A + - AA + - AAA + duration: + $ref: '#/components/schemas/Duration' + routeProtocal: + type: string + NetworkUpdate: + description: Base Connection Entity structure + type: object + properties: + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + sla: + type: string + enum: + - A + - AA + - AAA + + examples: + siteToCloudVPNFeasibilityAssessmentRequest: + summary: Assesment Sample 1 + description: Feasibility assessment sample + value: + isProtected: true + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + guaranteeBandwidth: 20 + duration: + value: 6 + unit: days + + siteToCloudVPNFeasibilityAssessmentResponse: + summary: Assesment Sample 1 + description: Feasibility assessment sample + value: + waitdays: 1 + sla: A + rent: + amount: 2000 + currency: GBP + siteToCloudVPNCreateConnectionRequest: + summary: Create Connection Sample 1 + description: Create Connection request sample + value: + isProtected: true + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + guaranteeBandwidth: 20 + duration: + value: 6 + unit: days + + siteToCloudVPNCreateConnectionResponse: + summary: Create Connection Sampl 1 + description: Create Connection response sample + value: + serviceId: 111111 + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + resourceGroupId: 12121 + cloudGatewayIP: 1.2.3.4 + siteToCloudVPNUpdateConnectionRequest: + summary: Update Connection Sample 1 + description: Update Connection request sample + value: + serviceId: 111111 + guaranteeBandwidth: 10 + sla: A + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic500: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Internal server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: Internal server error while processing request. +``` diff --git a/marked/MultiPointVPN/documentation/API_documentation/README/raw.md b/marked/MultiPointVPN/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/MultiPointVPN/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/MultiPointVPN/documentation/SupportingDocuments/README/raw.md b/marked/MultiPointVPN/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/MultiPointVPN/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/NetworkAccessManagement/README/raw.md b/marked/NetworkAccessManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..30cadd73e6615a5fe25508fb09a9a7f89e98ee4e --- /dev/null +++ b/marked/NetworkAccessManagement/README/raw.md @@ -0,0 +1,38 @@ + + + + + + + + + +# NetworkAccessManagement + +Sandbox API Repository to describe, develop, document, and test the NetworkAccessManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/5wCzHQ) + +## Scope +* Service APIs for “Network Access Management” of Home Devices (see APIBacklog.md) +* It provides the customer with the ability to: + * manage fixed devices provided by network operators that reside at customer premises. +* Describe, develop, document, and test the APIs (with 1-2 Telcos) +* Started: May 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96846363178?password=9ebebe6c-c59c-42be-a709-7d5fd42fb626) + * Schedule: Bi-weekly on Fridays at 8AM MDT / 4PM CEST + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/ez3e). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/NetworkAccessManagement/code/API_definitions/README/raw.md b/marked/NetworkAccessManagement/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f57b4609ee0d649500883631cd83c00675c82dad --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/README/raw.md @@ -0,0 +1,199 @@ +# Network Access Management API Definitions + +This directory contains the OpenAPI specifications for the Network Access Management API, organized into modular components for better maintainability and reusability. + +## Overview + +The API definitions have been restructured from a monolithic approach to a modular, component-based architecture. This allows for better code reuse, easier maintenance, and cleaner separation of concerns. + +## Folder Structure + +``` +API_definitions/ +├── README.md # This file (authoring & process docs) +├── redocly.yaml # Lint/bundle configuration (Redocly CLI) +├── network-access-management.yaml # Source API spec with $ref references (committed on main) +├── common/ +│ └── CAMARA_common.yaml # Shared CAMARA-style error responses +└── modules/ # Modular domain-focused component files + ├── NAM_Common.yaml # Shared primitives (UUID, DateTime, ResourceAudit, securitySchemes) + ├── AccessDetail.yaml # Discriminated access detail variants (Wi-Fi, Thread) + ├── Capabilities.yaml # Device capability schemas + ├── Policy.yaml # Trust Domain policy schemas (maxDevices, bandwidth, egress) + ├── NetworkAccessDevices/ # Network Access Device resource schemas + ├── RebootRequests/ # Reboot Request lifecycle schemas + ├── Services/ # Service and ServiceSite schemas + └── TrustDomains/ # Trust Domain & related capability schemas +``` + +## Architecture Rationale + +### Why Multiple Files? + +**Before:** Single monolithic OpenAPI file (`network-access-management.yaml`) +- ✅ Simple to understand initially +- ❌ Became very large (2000+ lines) +- ❌ Hard to maintain and review +- ❌ Schema duplication across different APIs +- ❌ Merge conflicts in collaborative development +- ❌ No reusability between different API specifications + +**After:** Modular component-based structure +- ✅ Each file has a single, clear responsibility +- ✅ Reusable schemas can be shared across APIs +- ✅ Easier to review and maintain individual components +- ✅ Parallel development by different team members +- ✅ Clear separation of concerns +- ✅ Smaller, focused files + +### Component Breakdown + +| File | Purpose | Reusability | +|------|---------|-------------| +| `Common.yaml` | Base types (UUID, DateTime, ErrorInfo) | High - used across all APIs | +| `Policy.yaml` | Trust Domain governance policies | Medium - Trust Domain specific | +| `AccessDetail.yaml` | Network access configurations | Medium - Network-related APIs | +| `TrustDomains.yaml` | Core Trust Domain schemas | Low - Trust Domain specific | + +## Bundling and Validation + +### Key Constraint: Bundled Files Are Not Committed on Main + +Per the [CAMARA Consumption and Bundling Design](https://github.com/camaraproject/Commonalities/blob/main/documentation/Commonalities-Consumption-and-Bundling-Design.md), **bundled (standalone) API definitions are never committed on `main`**. The committed `network-access-management.yaml` retains its `$ref` references to `common/` and `modules/`. Bundled standalone OAS files are produced only on release branches/tags and for local validation. + +This avoids merge conflicts in the large bundled output and keeps `main` as the single source of truth for modular schema authoring. + +Bundled output files (`*-bundled.yaml`) are listed in `.gitignore`. + +### Prerequisites + +Install Redocly CLI: +```bash +npm install -g @redocly/cli +``` + +### Linting + +Validate the spec and all referenced modules resolve correctly: +```bash +cd code/API_definitions +redocly lint network-access-management.yaml +``` + +### Local Bundling (for Validation or Tooling) + +To produce a fully resolved, standalone OAS file locally: +```bash +cd code/API_definitions +redocly bundle network-access-management.yaml --output network-access-management-bundled.yaml +``` + +The bundled file is useful for: +- Importing into API tools (Swagger UI, Postman, etc.) +- Validating the fully resolved spec with external validators +- Generating SDKs or documentation locally + +**Do not commit `*-bundled.yaml` files to `main`.** They are git-ignored. + +### Bundling Configuration + +The `redocly.yaml` file contains: +- **Linting rules** - Ensures consistency and quality +- **File resolution** - Allows `.yaml` and `.yml` extensions + +Key bundling features: +- Resolves all `$ref` references to external files +- Validates schema compatibility +- Generates self-contained OpenAPI specifications +- Preserves examples and documentation + +## File Purposes + +### API Specification + +- **`network-access-management.yaml`** - Source API specification with `$ref` references to `common/` and `modules/`. This is the file committed on `main`. Bundling resolves these refs into a standalone OAS file for release branches and local tooling. + +### Component Files + +- **`common/CAMARA_common.yaml`** - Shared CAMARA-style error responses and common schemas +- **`modules/NAM_Common.yaml`** - Shared fundamental types (UUID, DateTime, ResourceAudit, securitySchemes) +- **`modules/Policy.yaml`** - Trust Domain policy schemas (maxDevices, bandwidth limits, egress rules) +- **`modules/AccessDetail.yaml`** - Network access configuration schemas (Wi-Fi, Thread, security modes) +- **`modules/Capabilities.yaml`** - Device capability schemas +- **`modules/TrustDomains/TrustDomains.yaml`** - Core Trust Domain schemas and examples +- **`modules/NetworkAccessDevices/NetworkAccessDevices.yaml`** - Network Access Device resource schemas +- **`modules/RebootRequests/RebootRequests.yaml`** - Reboot Request lifecycle schemas +- **`modules/Services/Services.yaml`** - Service schemas +- **`modules/Services/ServiceSites.yaml`** - Service Site schemas + +## Best Practices + +### When to Create New Component Files +- **High reusability** - Schemas used by multiple APIs +- **Logical grouping** - Related schemas that form a cohesive unit +- **Size management** - When a file exceeds ~500 lines + +### Schema Design Guidelines +- Use `$ref` for external schema references +- Keep examples close to their schemas +- Use YAML anchors for internal reuse within files +- Document inheritance and discriminator patterns clearly + +### Example Cross-Reference Limitations + +**Important:** While schemas can be easily shared across files using `$ref`, examples have significant limitations in the distributed component model: + +#### The Problem +```yaml +# ❌ This does NOT work - cannot use $ref inside example values +TrustDomainExample: + summary: Trust Domain with Wi-Fi access + value: + name: "My Network" + accessDetails: + - $ref: "modules/AccessDetail.yaml#/components/examples/WiFiExample/value" # Invalid! +``` + +#### The Solutions + +**Option 1: Local Example Duplication (Recommended)** +```yaml +# ✅ Define examples locally where they're used +TrustDomainExample: + summary: Trust Domain with Wi-Fi access + value: + name: "My Network" + accessDetails: + - accessType: "Wi-Fi" + ssid: "my-network" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" +``` + +**Option 2: YAML Anchors (Within Same File Only)** +```yaml +# ✅ Use anchors for reuse within the same file +_wifi_example: &wifi-access + accessType: "Wi-Fi" + ssid: "my-network" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + +components: + examples: + TrustDomainExample: + value: + accessDetails: + - *wifi-access # Reuse within same file +``` + +**Option 3: Component-Level Example References** +```yaml +# ✅ Reference complete examples at component level (not within values) +WiFiAccessExample: + $ref: "modules/AccessDetail.yaml#/components/examples/WiFiAccessDetailWPA2Personal" + +# But you still can't compose these inside other example values +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/common/CAMARA_common/raw.md b/marked/NetworkAccessManagement/code/API_definitions/common/CAMARA_common/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..12b30418ac12c986514fbacc3c220a7d8c10a17b --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/common/CAMARA_common/raw.md @@ -0,0 +1,775 @@ +# CAMARA_common + +```yaml +# This file was pulled from https://github.com/camaraproject/Commonalities/blob/r3.4/artifacts/CAMARA_common.yaml +# in order to reference Commonalities models directly from spec files using $ref statements. +# +# IMPORTANT: This file has been modified in this repo in order to address linter warnings/errors that +# occurred in examples that referenced generic placeholder values like {{SPECIFIC_CODE}} or {{SPECIFIC_CODE_MESSAGE}}. +# The original file was using { { SPECIFIC_CODE } } in examples which had two issues. First, it's not quoted so it +# conform to the enum type (string). Second, even when quoted, the extraneous spaces inside the curly braces made it +# not conform to the pattern defined for that field. The modifications made were to remove any such placeholder entries +# from the examples, while leaving the rest of the example intact. +openapi: 3.0.3 +info: + title: CAMARA common data types + description: Common data types for CAMARA APIs + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.1 + x-camara-commonalities: 0.6 + +paths: {} +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + required: + - startDate + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + responses: + ####################################################### + ####################################################### + # ERROR RESPONSE SCHEMA TEMPLATE + # - Objective: Make normative error `status` and `code` values + # - Schema Template rationale: + # - The `allOf` in content.application/json.schema allows a combination of both the generic ErrorInfo schema and the specific schema for this error response, + # which validates that `status` and `code` have only the specified values. + # This `allOf` is used without discriminator because it does not imply any hierarchy between the models, just 2 schemas that must be independently validated. + ####################################################### + # ErrorResponseSchema: + # ... + # content: + # application/json: + # schema: + # allOf: + # - $ref: '#/components/schemas/ErrorInfo' + # - type: object + # properties: + # status: + # enum: + # - + # code: + # enum: + # - + # - + # examples: + # ExampleKey1: + # value: + # status: + # code: + # message: + # ExampleKey2: + # value: + # status: + # code: + # message: + ####################################################### + ####################################################### + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 405 + code: + enum: + - METHOD_NOT_ALLOWED + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 406 + code: + enum: + - NOT_ACCEPTABLE + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by the client through `Accept-*` headers. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic412: + description: Failed precondition + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 412 + code: + enum: + - FAILED_PRECONDITION + examples: + GENERIC_412_FAILED_PRECONDITION: + description: Indication by the API Server that the request cannot be processed in current system state + value: + status: 412 + code: FAILED_PRECONDITION + message: Request cannot be executed in the current system state. + Generic415: + description: Unsupported Media Type + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 415 + code: + enum: + - UNSUPPORTED_MEDIA_TYPE + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Payload format of the request is in an unsupported format by the Server. Should not happen + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as far as possible to get the objective to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 502 + code: + enum: + - BAD_GATEWAY + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 504 + code: + enum: + - TIMEOUT + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/modules/AccessDetail/raw.md b/marked/NetworkAccessManagement/code/API_definitions/modules/AccessDetail/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..66e750f5da12371072ccb9c52fd8deda9082e73f --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/modules/AccessDetail/raw.md @@ -0,0 +1,229 @@ +# AccessDetail + +```yaml +# This file defines the AccessDetail schema model for different network access types. +# It includes Wi-Fi and Thread access details with various security modes. + +components: + schemas: + # Base security mode schemas (unchanged) + WpaPersonalDetail: + type: object + description: WPA Personal security mode configuration for Wi-Fi networks. + properties: + password: + type: string + writeOnly: true + minLength: 8 + maxLength: 255 + pattern: "^[\\x20-\\x7E]{8,63}$" + description: The password for the WPA Personal Wi-Fi network + example: &wpa-personal-password "my-password" + securityModeType: + type: string + enum: + - WPA2-Personal + - WPA2-WPA3-Personal + - WPA3-Personal + description: | + The security mode type for the WPA Personal Wi-Fi network. + Leave blank to auto-select. + example: &wpa-personal-security-mode-type "WPA3-Personal" + additionalProperties: false + required: + - password + example: &wpa-personal + password: *wpa-personal-password + securityModeType: *wpa-personal-security-mode-type + + WpaEnterpriseDetail: + type: object + description: WPA Enterprise security mode configuration for Wi-Fi networks. + properties: + authServer: + type: string + maxLength: 255 + description: The authentication server for the WPA Enterprise Wi-Fi network + example: &wpa-enterprise-auth-server "1.2.3.4" + securityModeType: + type: string + enum: + - WPA2-Enterprise + - WPA3-Enterprise + description: The security mode type for the WPA Enterprise Wi-Fi network + example: &wpa-enterprise-security-mode-type "WPA3-Enterprise" + additionalProperties: false + required: + - securityModeType + example: &wpa-enterprise + authServer: *wpa-enterprise-auth-server + securityModeType: *wpa-enterprise-security-mode-type + + # Flattened concrete implementations for Wi-Fi + WiFiWpaPersonalAccessDetail: + type: object + description: Complete access details for Wi-Fi networks using WPA Personal security mode. + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_PERSONAL" + example: "Wi-Fi:WPA_PERSONAL" + ssid: + type: string + minLength: 2 + maxLength: 32 + pattern: "^(?! )[\\x20-\\x7E]{2,32}(?- + List of devices to reboot. When undefined, the reboot targets the 'default' device (simple use case that + wouldn't use locations or devices). Throws an error when creating if there is no 'default' device. + example: *device-id-list + + RebootRequest: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceIdentifier" + - $ref: "#/components/schemas/RebootRequestCreate" + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceAudit" + - type: object + properties: + id: + readOnly: true + createdAt: + readOnly: true + createdBy: + readOnly: true + modifiedAt: + readOnly: true + modifiedBy: + readOnly: true + required: + - devices + description: Represents a reboot request for one or more network access devices. + + RebootRequestList: + type: array + items: + $ref: "#/components/schemas/RebootRequest" + + examples: + RebootRequestCreateImmediateDefaultDevice: + summary: Example of a Reboot Request for immediate reboot + value: + message: "reboot to correct performance" + + RebootRequestCreateScheduledMultipleDevices: + summary: Example of a Reboot Request for scheduled reboot of multiple devices + value: + message: "Scheduled reboot for maintenance" + atTime: *date-time + devices: *device-id-list + + RebootRequestResponseInferred: + summary: Response after inferred default device reboot request + value: + id: *uuid-example-1 + message: "reboot to correct performance" + devices: + - *device-uuid-1 + atTime: *date-time + createdAt: *date-time + createdBy: *created-by-example + modifiedAt: *date-time + modifiedBy: *modified-by-example + + RebootRequestResponseExplicit: + summary: Response after explicit multi-device reboot request + value: + id: *uuid-example-2 + message: "scheduled maintenance reboot" + devices: *device-id-list + atTime: *date-time + createdAt: *date-time + createdBy: *created-by-example + modifiedAt: *date-time + modifiedBy: *modified-by-example +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites/raw.md b/marked/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..64d9a7f7552d2581b107aa03f0465ac1fa28d4b7 --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites/raw.md @@ -0,0 +1,71 @@ +# ServiceSites + +```yaml +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + uuid-example-2: &uuid-example-2 "123e4567-e89b-12d3-a456-426614174000" + property-address-example: &property-address-example + id: *uuid-example + addressLine1: "123 Main St" + addressLine2: "Suite 456" + streetNr: "123" + streetNrSuffix: "A" + streetNrLast: "125" + streetNrLastSuffix: "B" + streetName: "Main" + subUnitType: "Apartment" + subUnitNr: "A12" + levelType: "Floor" + levelNr: "3" + buildingName: "Sunset Towers" + privateStreetName: "Private Rd" + locality: "Example Locality" + city: "Example State" + stateOrProvince: "EX" + country: "United States" + postCode: "12345" + postCodeExtension: "6789" + +components: + schemas: + ServiceSite: + type: object + description: A Service Site represents a subscriber location associated with one or more Network Access Devices. Implementations MAY provide geographic coordinates, postal address data, or both, depending on local regulatory and operational requirements. + properties: + id: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/UUID" + readOnly: true + name: + type: string + description: The name of the service site. + maxLength: 64 + example: &service-site-name "Example Service Site 1" + description: + type: string + description: A textual description of the service site. + maxLength: 64 + example: &service-site-description "This is the first example service site" + location: + type: object + description: Geographic location information for the service site, including coordinates and/or property address. + properties: + geographicPoint: + $ref: "../../common/CAMARA_common.yaml#/components/schemas/Point" + propertyAddress: + $ref: "../NAM_Common.yaml#/components/schemas/PropertyAddress" + example: &service-site-location + geographicPoint: + latitude: 50.735851 + longitude: 7.10066 + propertyAddress: *property-address-example + required: + - id + example: &service-site + id: *uuid-example + name: *service-site-name + description: *service-site-description + location: *service-site-location +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/modules/Services/Services/raw.md b/marked/NetworkAccessManagement/code/API_definitions/modules/Services/Services/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..abe11f54878c5c35796634ca5a0bf18dd142bbd6 --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/modules/Services/Services/raw.md @@ -0,0 +1,105 @@ +# Services + +```yaml +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + uuid-example-2: &uuid-example-2 "123e4567-e89b-12d3-a456-426614174000" + uuid-example-3: &uuid-example-3 "123e4567-e89b-12d3-a456-426614174001" + property-address-example: &property-address-example + id: *uuid-example + addressLine1: "123 Main St" + addressLine2: "Suite 456" + streetNr: "123" + streetNrSuffix: "A" + streetNrLast: "125" + streetNrLastSuffix: "B" + streetName: "Main" + subUnitType: "Apartment" + subUnitNr: "A12" + levelType: "Floor" + levelNr: "3" + buildingName: "Sunset Towers" + privateStreetName: "Private Rd" + locality: "Example Locality" + city: "Example State" + stateOrProvince: "EX" + country: "United States" + postCode: "12345" + postCodeExtension: "6789" + service-site-example: &service-site-example + id: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + name: "Primary Residence" + description: "123 Main Street" + location: *property-address-example + +components: + parameters: + serviceId: + name: serviceId + in: path + description: The unique identifier of the Service. If the service exists but the caller lacks permission to access it, the API returns 403. + required: true + schema: + $ref: "#/components/schemas/ServiceId" + + schemas: + ServiceId: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/UUID" + description: | + A unique identifier that represents a service account associated with this resource. + + Must be a valid UUID as defined by RFC 4122 (versions 1-5) using only lowercase hexadecimal characters. + + Service: + type: object + description: | + A service represents a logical commercial subscription or account relationship + between a network operator and a subscriber. This may correspond to residential, + commercial, public Wi-Fi, or other service types. + properties: + id: + $ref: "#/components/schemas/ServiceId" + name: + type: string + maxLength: 64 + description: Optional friendly name for the service + example: "Main Home Internet" + description: + type: string + maxLength: 255 + description: Optional description of the service + example: "Internet subscription for primary residence" + serviceSite: + # Optional. Present for location-specific services (e.g., residential, office), absent for general services (e.g., public Wi-Fi) + $ref: "./ServiceSites.yaml#/components/schemas/ServiceSite" + required: + - id + example: + id: *uuid-example + name: "Main Home Internet" + description: "Internet subscription for primary residence" + serviceSite: + id: *uuid-example-2 + name: "Primary Residence" + description: "123 Main Street" + + ServiceList: + type: array + description: A list of services accessible to the calling identity + items: + $ref: "#/components/schemas/Service" + example: + - id: *uuid-example + name: "Main Home Internet" + description: "Internet subscription for primary residence" + serviceSite: + id: *uuid-example-2 + name: "Primary Residence" + description: "123 Main Street" + - id: *uuid-example-3 + name: "Vacation Home Internet" + description: "Internet subscription for vacation home" +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities/raw.md b/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e0cdda1cdc50bef33e045d388ff719d0b569f06e --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities/raw.md @@ -0,0 +1,284 @@ +# TrustDomainCapabilities + +```yaml +components: + schemas: + TrustDomainCapabilities: + type: object + properties: + supportedAccessTypes: + type: array + description: List of supported access types and their variants + items: + $ref: "#/components/schemas/SupportedAccessType" + minItems: 1 + supportedPolicies: + type: object + description: Map of supported policy types to their capability details + properties: + maxDevices: + $ref: "#/components/schemas/MaxDevicesPolicyCapability" + maxDomainDownstreamRate: + $ref: "#/components/schemas/BandwidthPolicyCapability" + maxDomainUpstreamRate: + $ref: "#/components/schemas/BandwidthPolicyCapability" + egressAllowedList: + $ref: "#/components/schemas/EgressPolicyCapability" + example: + maxDevices: + maxValue: 100 + minValue: 1 + maxDomainDownstreamRate: + maxValue: 1000000000 + minValue: 1000000 + required: + - supportedAccessTypes + description: Describes the Trust Domain configuration capabilities supported by this API provider + + SupportedAccessType: + type: object + description: Access type capabilities with discriminated properties based on accessType. Represents the configuration options supported by the API provider for a given access type. This is distinct from AccessDetail, which represents the configuration requested by an API client. + properties: + accessType: + type: string + enum: + - "Wi-Fi:WPA_PERSONAL" + - "Wi-Fi:WPA_ENTERPRISE" + - "Thread:STRUCTURED" + - "Thread:TLV" + description: The supported access type identifier (must match POST endpoint values) + oneOf: + - $ref: "#/components/schemas/SupportedWiFiWpaPersonalAccessType" + - $ref: "#/components/schemas/SupportedWiFiWpaEnterpriseAccessType" + - $ref: "#/components/schemas/SupportedThreadStructuredAccessType" + - $ref: "#/components/schemas/SupportedThreadTlvAccessType" + discriminator: + propertyName: accessType + mapping: + "Wi-Fi:WPA_PERSONAL": "#/components/schemas/SupportedWiFiWpaPersonalAccessType" + "Wi-Fi:WPA_ENTERPRISE": "#/components/schemas/SupportedWiFiWpaEnterpriseAccessType" + "Thread:STRUCTURED": "#/components/schemas/SupportedThreadStructuredAccessType" + "Thread:TLV": "#/components/schemas/SupportedThreadTlvAccessType" + required: + - accessType + + SupportedWiFiWpaPersonalAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_PERSONAL" + example: "Wi-Fi:WPA_PERSONAL" + wifiProperties: + $ref: "#/components/schemas/WiFiAccessTypeProperties" + required: + - accessType + - wifiProperties + description: Wi-Fi WPA Personal access type capabilities + + SupportedWiFiWpaEnterpriseAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_ENTERPRISE" + example: "Wi-Fi:WPA_ENTERPRISE" + wifiProperties: + $ref: "#/components/schemas/WiFiAccessTypeProperties" + required: + - accessType + - wifiProperties + description: Wi-Fi WPA Enterprise access type capabilities + + SupportedThreadStructuredAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Thread:STRUCTURED" + example: "Thread:STRUCTURED" + threadProperties: + $ref: "#/components/schemas/ThreadAccessTypeProperties" + required: + - accessType + - threadProperties + description: Thread structured access type capabilities + + SupportedThreadTlvAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Thread:TLV" + example: "Thread:TLV" + threadProperties: + $ref: "#/components/schemas/ThreadAccessTypeProperties" + required: + - accessType + - threadProperties + description: Thread TLV access type capabilities + + # Explicit policy capability schemas + MaxDevicesPolicyCapability: + type: object + properties: + maxValue: + type: integer + minimum: 1 + description: Maximum number of devices allowed + example: 100 + minValue: + type: integer + minimum: 1 + description: Minimum number of devices allowed + example: 1 + required: + - maxValue + - minValue + description: Capabilities for maximum devices policy + + BandwidthPolicyCapability: + type: object + properties: + maxValue: + type: integer + minimum: 1 + description: Maximum bandwidth value in bits per second + example: 1000000000 + minValue: + type: integer + minimum: 1 + description: Minimum bandwidth value in bits per second + example: 1000000 + required: + - maxValue + - minValue + description: Capabilities for bandwidth control policies + + EgressPolicyCapability: + type: object + properties: + maxEntries: + type: integer + minimum: 1 + description: Maximum number of allowed egress destinations + example: 50 + supportedDestinationTypes: + type: array + items: + type: string + enum: ["IP", "FQDN", "CIDR"] + description: Supported destination address formats + example: ["IP", "FQDN", "CIDR"] + required: + - maxEntries + - supportedDestinationTypes + description: Capabilities for egress allowed list policy + + # Explicit access type property schemas + WiFiAccessTypeProperties: + type: object + properties: + ssidRequired: + type: boolean + description: Whether SSID must be provided (false if can be inferred) + example: true + supportedSecurityModes: + type: array + items: + type: string + enum: + - "WPA2-Personal" + - "WPA3-Personal" + - "WPA2-WPA3-Personal" + - "WPA2-Enterprise" + - "WPA3-Enterprise" + description: Supported Wi-Fi security mode types + example: ["WPA2-Personal", "WPA3-Personal"] + passwordConstraints: + $ref: "#/components/schemas/PasswordConstraints" + authServerRequired: + type: boolean + description: Whether authentication server must be specified for Enterprise modes + example: false + description: Wi-Fi specific access type properties + + ThreadAccessTypeProperties: + type: object + properties: + supportedChannels: + type: object + properties: + min: + type: integer + minimum: 11 + maximum: 26 + description: Minimum supported Thread channel + example: 11 + max: + type: integer + minimum: 11 + maximum: 26 + description: Maximum supported Thread channel + example: 26 + required: + - min + - max + description: Range of supported Thread channels + networkKeyFormat: + type: string + enum: ["32-hex-digits"] + description: Required format for Thread network keys + example: "32-hex-digits" + networkNameConstraints: + type: object + properties: + minLength: + type: integer + minimum: 1 + example: 1 + maxLength: + type: integer + minimum: 1 + example: 16 + required: + - minLength + - maxLength + description: Constraints on Thread network names + maxDatasetLength: + type: integer + minimum: 1 + description: Maximum length for TLV operational dataset (applies to Thread:TLV) + example: 255 + description: Thread specific access type properties + + PasswordConstraints: + type: object + properties: + minLength: + type: integer + minimum: 8 + description: Minimum password length + example: 8 + maxLength: + type: integer + minimum: 1 + description: Maximum password length + example: 63 + requireSpecialCharacters: + type: boolean + description: Whether special characters are required + example: false + required: + - minLength + - maxLength + description: Password validation constraints +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains/raw.md b/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7227b10fe800c2e01b4464740e4dda3013e4d552 --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains/raw.md @@ -0,0 +1,269 @@ +# TrustDomains + +```yaml +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + service-uuid-example: &service-uuid-example "123e4567-e89b-12d3-a456-426614174000" + wifi-wpa2-personal-basic-example: &wifi-wpa2-personal-basic-example + accessType: "Wi-Fi:WPA_PERSONAL" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + + wifi-wpa2-personal-example: &wifi-wpa2-personal-example + accessType: "Wi-Fi:WPA_PERSONAL" + ssid: "my-ssid" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + + wifi-wpa3-personal-example: &wifi-wpa3-personal-example + accessType: "Wi-Fi:WPA_PERSONAL" + ssid: "my-ssid" + securityMode: + password: "my-password" + securityModeType: "WPA3-Personal" + + thread-structured-example: &thread-structured-example + accessType: "Thread:STRUCTURED" + channel: 13 + extendedPanId: "d63e8e3e495ebbc3" + networkKey: "dfd34f0f05cad978ec4e32b0413038ff" + networkName: "Spec-Thread-B3AF" + panId: "d63e" + + thread-tlv-example: &thread-tlv-example + accessType: "Thread:TLV" + mode: tlv + operationalDataset: "0e08000000000000010010000102030405060708090a0b0c0d0e0f" + + max-devices-policy-example: &max-devices-policy-example + maxDevices: 10 + + max-bandwidth-policy-example: &max-bandwidth-policy-example + maxDomainDownstreamRate: + value: 1000000 + unit: Kbps + maxDomainUpstreamRate: + value: 500000 + unit: Kbps + + egress-allowed-list-policy-example: &egress-allowed-list-policy-example + egressAllowedList: + - "api.vendor.com" + - "updates.vendor.com" + + created-by-example: &created-by-example "550e8400-e29b-41d4-a716-446655440000" + modified-by-example: &modified-by-example "660e8400-e29b-41d4-a716-446655440000" + modified-by-example-2: &modified-by-example-2 "770e8400-e29b-41d4-a716-446655440000" + +components: + + parameters: + trustDomainId: + name: trustDomainId + in: path + required: true + schema: + $ref: "../NAM_Common.yaml#/components/schemas/UUID" + description: ID of the Trust Domain. If the Trust Domain exists but the caller lacks permission to access it, the API returns 403. + + schemas: + + TrustDomainUpdate: + type: object + description: Represents the updatable fields of a trust domain within the network access management system. + properties: + name: + type: string + description: Human-readable name for the trust domain. + example: "Primary WiFi Network" + description: + type: string + description: Detailed description of the trust domain. + example: "Primary home WiFi Network for all devices" + enabled: + type: boolean + description: Indicates whether the trust domain is currently enabled. + example: true + expiration: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/DateTime" + - description: | + The expiration date and time of the network. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows + 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + + If omitted, the trust domain will not automatically expire. + policies: + $ref: "../Policy.yaml#/components/schemas/Policies" + accessDetails: + type: array + # Each item grants access for a device to this Trust Domain, scoped by the associated AP/network access device or AP group. + description: | + A list of access configurations that define how end-user devices may join the + Trust Domain. Each entry represents one access type (e.g., Wi-Fi WPA Personal, + Wi-Fi WPA Enterprise, Thread Structured, Thread TLV). + + **Multiplicity and Uniqueness** + - A Trust Domain MUST contain at least one accessDetail entry. + - Each `accessType` SHOULD appear at most once. If multiple entries of the same + `accessType` are provided, the API provider MAY reject the request. + - Order of entries has no semantic meaning. + + **Creation and Update Semantics** + - On creation (POST), the full list of accessDetails MUST be provided. + - On update (PATCH), the list replaces the previous list entirely when included. + Partial merge semantics are not defined; clients MUST supply the complete + desired configuration for this field. + - To remove all access types, clients MAY provide an empty array, although the + API provider MAY reject configurations that result in no valid admittance + method for the Trust Domain. + + **Validation Expectations** + - The API provider MUST validate that the requested access types and their + properties conform to the provider's advertised capabilities + (via GET /trust-domains/capabilities). + - Providers MAY enforce additional constraints (e.g., SSID uniqueness, + channel restrictions, Thread dataset rules) based on local policy. + + **Deployment Behavior** + - All Network Access Devices configured with this Trust Domain MUST apply all + supplied accessDetails entries, unless the provider's capabilities indicate + that certain access types are not supported on specific devices. + items: + $ref: "../AccessDetail.yaml#/components/schemas/AccessDetail" + minItems: 1 + + TrustDomainCreate: + allOf: + - $ref: "#/components/schemas/TrustDomainUpdate" + description: Represents the creation of a new trust domain within the network access management system. + required: + - name + - enabled + - accessDetails + - serviceId + properties: + serviceId: + $ref: "../Services/Services.yaml#/components/schemas/ServiceId" + + TrustDomain: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceIdentifier" + - $ref: "#/components/schemas/TrustDomainCreate" + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceAudit" + - type: object + properties: + id: + readOnly: true + createdAt: + readOnly: true + createdBy: + readOnly: true + modifiedAt: + readOnly: true + modifiedBy: + readOnly: true + description: Represents a trust domain within the network access management system. + + + examples: + + TrustDomainCreateWpa2Personal: + summary: Create a Trust Domain with WPA2-Personal Wi-Fi access. + value: + name: "Primary WiFi Network" + description: "Request defines a Trust Domain with WPA2-Personal Wi-Fi access. The request specifies an SSID, implying the SSID is created on the network infrastructure." + enabled: true + accessDetails: + - <<: *wifi-wpa2-personal-example + serviceId: *service-uuid-example + + TrustDomainCreateInferredSsid: + summary: Create a Trust Domain with inferred SSID Wi-Fi access. + value: + name: "Inferred SSID Network" + description: "Request defines a Trust Domain with inferred SSID Wi-Fi access. The request omits the SSID, implying the Trust Domain is applied to an existing SSID on the network infrastructure." + enabled: true + accessDetails: + - accessType: "Wi-Fi:WPA_PERSONAL" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + serviceId: *service-uuid-example + + TrustDomainCreateEphemeral: + summary: Create a Trust Domain with ephemeral access details. + value: + name: "Ephemeral Network" + description: "Request defines a Trust Domain with ephemeral access details." + enabled: true + accessDetails: + - <<: *wifi-wpa3-personal-example + expiration: "2024-12-31T23:59:59Z" + policies: + <<: *max-devices-policy-example + serviceId: *service-uuid-example + + TrustDomainCreateThreadStructured: + summary: Create a Trust Domain with Thread structured access details. + value: + name: "Thread Structured Network" + description: "Request defines a Trust Domain with Thread structured access details." + enabled: true + accessDetails: + - <<: *thread-structured-example + serviceId: *service-uuid-example + + TrustDomainCreateQoSPolicies: + summary: Create a Trust Domain with QoS policies. + value: + name: "QoS Policy Network" + description: "Request defines a Trust Domain with QoS policies." + enabled: true + accessDetails: + - <<: *wifi-wpa3-personal-example + policies: + <<: *max-bandwidth-policy-example + serviceId: *service-uuid-example + + ## Example responses + TrustDomainResponseBasic: + summary: Basic Trust Domain Response + description: Example of a created Trust Domain with minimal details. + value: + id: *uuid-example + name: "Basic Trust Domain" + description: "A basic trust domain example" + enabled: true + accessDetails: + - <<: *wifi-wpa2-personal-example + serviceId: *service-uuid-example + createdAt: "2025-10-21T14:27:08.312Z" + createdBy: *created-by-example + modifiedAt: "2025-10-21T14:27:08.312Z" + modifiedBy: *modified-by-example + + TrustDomainResponseWiFiThread: + summary: Created Trust Domain (Wi-Fi + Thread) + description: Example of a created Trust Domain including Wi-Fi and Thread access details and populated policies. + value: + id: *uuid-example + name: "Primary WiFi Network" + description: "Primary home Wi-Fi Network for all devices" + enabled: true + expiration: "2025-10-21T14:27:08.312Z" + policies: + <<: *egress-allowed-list-policy-example + accessDetails: + - <<: *wifi-wpa3-personal-example + - <<: *thread-structured-example + serviceId: *service-uuid-example + createdAt: "2025-10-21T14:27:08.312Z" + createdBy: *created-by-example + modifiedAt: "2025-10-21T14:27:08.312Z" + modifiedBy: *modified-by-example-2 +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/network-access-management/raw.md b/marked/NetworkAccessManagement/code/API_definitions/network-access-management/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..749f82b6271500717f8c668990e284a488e90e2d --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/network-access-management/raw.md @@ -0,0 +1,742 @@ +# network-access-management + +```yaml +openapi: 3.0.3 + +info: + title: Home Devices - Network Access Management + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + description: | + Service enabling API for managing network operator supplied network access devices. This API's initial focus is on + managing **Trust Domains** and device reboot requests. + + # Introduction + A Trust Domain is a network access configuration where each configuration is for a logically separated Local + Area Network (LAN). API consumers can create, modify, or remove these networks which could be useful in + scenarios such as: + + - A property owner wants to create a temporary network for the duration of a short-term booking or long-term rental. + - A property manager wants to replicate the network access details across multiple network access devices at one or + more locations such as common areas, offices, etc. + - A security/privacy-minded user wants to create one or more networks for their guests or Internet-of-Thing (IoT) + network clients. + + A reboot request is simply a request to reboot a network operator supplied network access device. API consumers + can create these requests which could be useful in scenarios such as: + + - A property owner wants to recover from a faulty network state by rebooting a gateway device. + - A property manager wants to reboot multiple devices at one or more locations such as common areas, offices, etc. + + # Relevant Terms and Definitions + - **Trust Domain**: a declarative, intent-level grouping that defines which devices are permitted to communicate with each other as if they were on the same LAN and what high-level access policies apply to that group. + - **Reboot Request**: A request to reboot a network operator supplied network access device. + - **Network Access Device**: A network operator supplied network access device that supports network segmentation technologies. Multiple devices + that support LAN connectivity across the same Trust Domain (e.g., mesh Wi-Fi, Thread personal area network, + etc.) SHOULD be presented as a single device for implementations of this API. + - **API Provider**: Provider that implements this API. + - **Network Operator**: Service provider that has operational control of supporting devices. + - **Service Owner**: Customer of a network operator and resource owner with one or more devices that supports this + API across one or more service sites. + - **Service Site**: A distinct service owner location, as interpreted by the network operator, with one or more + devices. A service site typically has a one-to-one relationship with the mailing address of the location. Network + operators that support a single identity or interchangeable identities for multiple service sites at the same + mailing address (e.g., a residential and business account, an office and common area account, etc.) MUST provide + some distinction in the property address (e.g., attn: Home Office, attn: Common Area, etc.). Multiple service + sites, for the same mailing address, but for unrelated service owner identities, do not have this requirement. + - **End-User**: The user connecting to a Trust Domain with a network client. + - **Network Client**: End-user equipment connecting to a Trust Domain (e.g., laptop, phone, IoT device, etc.). + - **API Consumer**: A first- or third-party software system using this API. + + # API Functionality + This API allows API Consumers to manage Trust Domains and reboot network access devices. + + ### Authorization and authentication + + The "CAMARA Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ### Scopes + Scopes are used to protect the service owner's information and privacy. The general format is + `--`. A resource may be further broken down into `-` or + `-` for granular permissions. Scopes also control output information as opposed to just + authorizing endpoints. Each endpoint definition will clearly state what scopes are needed for access and which are + needed to access additional information. Below are some general rules for scopes in this API. + + - Regulated information, such as physical locations or hardware addresses of network devices, have special scopes. + Network operators are expected to follow any local regulations when sharing this information with an API client. + - Scopes have inheritance when one scope would otherwise require the inherited scope. + - Read scopes for one resource impacts the output of another resource when the requested resource has a relationship + with the first (e.g., listing networks on a device requires both device and network read scopes). + + | Scope | Description | + |-------|-------------| + | **network-access-management:trust-domains** | Manage the caller's own Trust Domains (create, modify, delete, view). | + | **network-access-management:trust-domains:read-all** | Read all Trust Domains belonging to the subscriber, including those created by other clients (requires subscriber consent). | + | **network-access-management:reboot** | Create, list, and manage Reboot Requests for owned devices. | + | **network-access-management:services:read** | List services accessible to the authenticated identity | + + ## General Usage + This API is intended for creating, modifying, or deleting Trust Domains using the `/trust-domains` endpoints + to build access detail configurations. The `/service-sites` endpoints are used for iterating over a service owner's + locations. The exact location may be requested with an additional scope to assist with reconciling information about + service sites when the API client operator has an existing relationship with the service owner. Similarly, the + `/devices` endpoints are used for iterating over and configuring a service owner's devices. The hardware address + may be requested for the same purpose of reconciling information from another source (e.g., database, persons with + physical device access, etc.). + + ## Comments for API Clients + + ### Reboot Requests + Reboot Requests provide a declarative mechanism for API clients to trigger an + immediate or scheduled reboot of one or more Network Access Devices associated + with a subscriber. The following clarifies expected behavior, device inference + rules, and recommended client patterns. + + #### Device Targeting + Clients MAY target devices in one of two ways: + + 1. **Explicit Targeting** + The client provides a `devices` array containing one or more device UUIDs. + This mode MUST be used when: + - multiple devices exist for the subscriber + - reboot is intended for a subset of devices + - the provider indicates that inference is unsupported + + 2. **Implicit (“Default Device”) Targeting** + Clients MAY omit the `devices` array to reboot a default device, if and only if: + - exactly one device is provisioned for the subscriber + - the provider supports inference + - the device is reboot-capable + + If inference fails, the request MUST be rejected (e.g., 400 INVALID_ARGUMENT or + 422 MISSING_IDENTIFIER). + + #### Behavior Guarantees + + - If `devices` is omitted and inference succeeds, the response MUST contain the + provider-resolved device list. + - Validation is atomic: if any device ID is invalid, unauthorized, or not + reboot-capable, the request MUST fail without side effects. + - Partial success is not allowed. + - Providers MAY reject duplicate reboot requests targeting the same devices and time. + + #### Interaction with Related Endpoints + + - `GET /network-access-devices` + Used to enumerate devices and their configuration. + + - `POST /reboot-requests` + Create a reboot request (immediate or scheduled). + + - `GET /reboot-requests/{id}` + Retrieve the status of a previously-created request. Implementations MAY extend + the status model over time. + + #### Recommended Client Flow + + 1. (Optional) Query device capabilities using `/network-access-devices`. + 2. If multiple devices exist or inference is unsupported, build an explicit + device list. + 3. Create the reboot request with immediate or scheduled execution (`atTime`). + 4. (Optional) Poll the individual reboot request status for asynchronous flows. + + ## Comments for Network Operators + The following comments are for Network Operators implementing this API. + + ### Auto-Deleting Trust Domains + When a Trust Domain is not configured on any device the network configuration and its identifier SHOULD be + auto-deleted. API clients MUST not be expected to delete Trust Domains not configured on any device. + + ### Mesh Systems + Mesh systems SHOULD be represented as a single device when implementing this API due to the undefined behavior of + LAN connectivity across multiple devices with the same Trust Domain. The recommendation is to use the gateway + hardware address of the mesh system when exposing that field, though the hardware address of any node in the mesh + may be used. If an end-user replaces the equipment, all existing Trust Domains SHOULD be synced to the new + device representing this mesh. Alternatively, a synthetic hardware address may also be used if the specification + for the address type allows. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/NetworkAccessManagement + +servers: + - url: "{apiRoot}/network-access-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Services + description: Operations to list network services accessible to the authenticated identity + - name: Trust Domains + description: Operations to Create and Manage Trust Domains + - name: Reboot Requests + description: | + Operations to Create and Manage Reboot Requests for Network Access Devices + +paths: + + /services: + get: + tags: + - Services + summary: Get all services accessible to the authenticated identity + security: + - openId: + - network-access-management:services:read + operationId: getServices + description: | + Returns all services accessible to the calling identity. Services represent + a logical commercial relationship between a subscriber and a network operator, + typically corresponding to a unique service account or subscription. + + This endpoint supports workflows where an API Consumer (e.g., AirBnB, Amazon) + has received subscriber authorization and must enumerate services to link with + Network Client Devices or Trust Domains. + + responses: + "200": + description: Contains all services associated with the identity + content: + application/json: + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/ServiceList" + "401": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic401" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + + + /services/{serviceId}: + get: + tags: + - Services + summary: Get a service by ID + security: + - openId: + - network-access-management:services:read + operationId: getService + description: | + Returns a specific service corresponding to the given `serviceId`. + + This can be used to inspect service metadata prior to using it in other + API operations such as Trust Domain creation. + + **Required Scopes:** + - `network-access-management:services:read` + + parameters: + - name: serviceId + in: path + required: true + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/ServiceId" + description: | + The ID of the service to retrieve. + + Must be a valid UUID as defined by RFC 4122 (versions 1-5) using only lowercase hexadecimal characters. + responses: + "200": + description: Information about the service + content: + application/json: + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/Service" + "401": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic401" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + + /trust-domains/capabilities: + get: + tags: + - Trust Domains + summary: Get Trust Domain capabilities + security: + - openId: + - network-access-management:trust-domains + operationId: getTrustDomainCapabilities + description: | + Retrieves the set of Trust Domain configuration capabilities supported by the API provider. + Capabilities describe supported access types, policy constraints, and configuration limits. + + This endpoint enables API clients to discover: + - Which access types are supported (Wi-Fi variants, Thread modes, etc.) + - What policy types are available + - Operational limits and constraints + - Advanced features and configuration options + + Use this endpoint before creating Trust Domains to ensure your configuration + is supported by the target API provider/network operator. + + responses: + "200": + description: Trust Domain capabilities supported by this API provider + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomainCapabilities.yaml#/components/schemas/TrustDomainCapabilities" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /trust-domains: + post: + tags: + - Trust Domains + summary: Create a new Trust Domain + security: + - openId: + - network-access-management:trust-domains + description: | + Creates and returns the new Trust Domain. + + operationId: createTrustDomain + requestBody: + description: Details of the Trust Domain to be created + required: true + content: + application/json: + schema: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomainCreate' + examples: + TrustDomainCreateWpa2Personal: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateWpa2Personal' + TrustDomainCreateInferredSsid: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateInferredSsid' + TrustDomainCreateThreadStructured: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateThreadStructured' + TrustDomainCreateEphemeral: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateEphemeral' + TrustDomainCreateQoSPolicies: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateQoSPolicies' + responses: + '201': + description: Trust Domain created successfully + content: + application/json: + schema: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain' + examples: + TrustDomainResponseBasic: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseBasic' + TrustDomainResponseWiFiThread: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseWiFiThread' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + get: + tags: + - Trust Domains + summary: Retrieves all Trust Domains visible to the calling API client + security: + - openId: + - network-access-management:trust-domains + - openId: + - network-access-management:trust-domains:read-all + operationId: getTrustDomains + description: | + Retrieves all Trust Domains visible to the calling API client. + + If the caller has `network-access-management:trust-domains`, the response is limited to + Trust Domains created by the caller. If the caller has `network-access-management:trust-domains:read-all`, + the response includes all Trust Domains associated with the subscriber. + responses: + + "200": + description: Contains information about all trust domains + content: + application/json: + schema: + type: array + items: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /trust-domains/{trustDomainId}: + parameters: + - $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/parameters/trustDomainId' + + get: + tags: + - Trust Domains + summary: Get a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + - openId: + - network-access-management:trust-domains:read-all + operationId: getTrustDomain + description: | + Retrieves the Trust Domain identified by the given ID. Visibility of this Trust Domain depends on the caller's scope and ownership: + - `trust-domains` restricts access to caller-owned Trust Domains. + - `trust-domains:read-all` allows retrieval of any Trust Domain associated with the subscriber. + + responses: + + "200": + description: Contains information about the specified trust domain + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + examples: + TrustDomainResponseBasic: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseBasic' + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + patch: + tags: + - Trust Domains + summary: Update a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + operationId: updateTrustDomain + description: | + Updates the Trust Domain identified by the given ID. Any changes are automatically applied to all network access devices where the Trust Domain is configured. + + requestBody: + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomainUpdate" + required: true + responses: + "200": + description: Contains information about the updated trust domain + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + delete: + tags: + - Trust Domains + summary: Delete a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + operationId: deleteTrustDomain + description: | + Deletes the Trust Domain identified by the given ID and removes its configuration from all network access devices where it is applied. + + responses: + "204": + description: Trust Domain deleted successfully + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /network-access-devices: + get: + tags: + - Reboot Requests + summary: Get all Network Access Devices associated with the service owner + security: + - openId: + - network-access-management:reboot + operationId: getNetworkAccessDevices + description: | + Retrieves all Network Access Devices associated with the subscriber that the caller is authorized to manage using the `network-access-management:reboot` scope. + responses: + "200": + description: Contains the list of network access devices + content: + application/json: + schema: + $ref: "modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/schemas/NetworkAccessDeviceList" + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /network-access-devices/{networkAccessDeviceId}: + get: + tags: + - Reboot Requests + summary: Get a specific Network Access Device + security: + - openId: + - network-access-management:reboot + operationId: getNetworkAccessDevice + description: | + Retrieves the Network Access Device that matches the given ID. + parameters: + - $ref: 'modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/parameters/networkAccessDeviceId' + responses: + "200": + description: Contains information about the specified network access device + content: + application/json: + schema: + $ref: "modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/schemas/NetworkAccessDevice" + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /reboot-requests: + post: + tags: + - Reboot Requests + summary: Create a new Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Creates a new Reboot Request targeting one or more Network Access Devices. + operationId: createRebootRequest + requestBody: + description: | + Creates a reboot request for one or more network access devices. Supports two targeting modes: + + Targeting modes: + - Inferred (implicit/default device): Omit the 'devices' array to request a reboot of the single + default device associated with the subscriber context. This is only valid when exactly one + device is eligible. If no default device exists or multiple devices are provisioned, the + request MUST be rejected (e.g. 400 INVALID_ARGUMENT or 422 MISSING_IDENTIFIER). + - Explicit (targeted devices): Provide a 'devices' array of one or more device UUIDs to request + reboots on those specific devices. Validation MUST fail if any supplied device ID is unknown, + not reboot-capable, or the caller lacks authorization. + + Scheduling: + - Immediate reboot: Omit 'atTime'. + - Scheduled reboot: Include 'atTime' (RFC 3339 with timezone). Time MUST be in the future; past + values SHOULD produce a 400 OUT_OF_RANGE error. + + Idempotency / duplication: + - Multiple identical pending reboot requests (same device set and same atTime) MAY be rejected + with 409 CONFLICT or collapsed by implementation. + + Error conditions (examples): + - 400 INVALID_ARGUMENT: Unsupported time format, too many device IDs, malformed UUID. + - 404 IDENTIFIER_NOT_FOUND: One or more device IDs not found. + - 403 PERMISSION_DENIED: Caller lacks scope or device ownership. + - 409 CONFLICT: Reboot already scheduled for the same devices and time. + - 422 MISSING_IDENTIFIER (implementation-specific): 'devices' omitted but no default device. + + Behavioral guarantees: + - If 'devices' omitted and inference succeeds, the response MUST reflect the resolved device list. + - If any device fails validation, no reboot request is created (atomic failure). + - Partial success is NOT permitted. + required: true + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequestCreate' + examples: + RebootRequestCreateImmediate: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/examples/RebootRequestCreateImmediateDefaultDevice' + RebootRequestCreateScheduled: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/examples/RebootRequestCreateScheduledMultipleDevices' + responses: + '201': + description: Reboot Request created successfully + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '422': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic422' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + get: + tags: + - Reboot Requests + summary: Get all Reboot Requests created by the calling API client + security: + - openId: + - network-access-management:reboot + operationId: getRebootRequests + description: | + This endpoint returns a list of Reboot Requests associated with the service owner created by the calling API client. + responses: + '200': + description: Contains information about all reboot requests + content: + application/json: + schema: + type: array + items: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + /reboot-requests/{rebootRequestId}: + parameters: + - $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/parameters/rebootRequestId' + + get: + tags: + - Reboot Requests + summary: Get a specific Reboot Request + security: + - openId: + - network-access-management:reboot + operationId: getRebootRequest + description: | + Retrieves the Reboot Request that matches the given ID. + responses: + '200': + description: Contains information about the specified Reboot Request + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + patch: + tags: + - Reboot Requests + summary: Update an existing Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Updates an existing Reboot Request to modify its scheduled time or cancel it. + operationId: updateRebootRequest + requestBody: + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequestUpdate' + required: true + responses: + '200': + description: Reboot Request updated successfully + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '422': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic422' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + delete: + tags: + - Reboot Requests + summary: Delete an existing Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Deletes an existing Reboot Request, cancelling the scheduled reboot if it has not yet occurred. + operationId: deleteRebootRequest + responses: + '204': + description: Reboot Request deleted successfully + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + +components: + securitySchemes: + openId: + $ref: 'modules/NAM_Common.yaml#/components/securitySchemes/openId' +``` diff --git a/marked/NetworkAccessManagement/code/API_definitions/redocly/raw.md b/marked/NetworkAccessManagement/code/API_definitions/redocly/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5b272c81c39170e1f2093ef2a6a08ad1052888c7 --- /dev/null +++ b/marked/NetworkAccessManagement/code/API_definitions/redocly/raw.md @@ -0,0 +1,14 @@ +# redocly + +```yaml +extends: + - recommended + +rules: + no-unused-components: "off" + no-empty-servers: "off" + +resolve: + file: + allowedFileExtensions: [".yaml", ".yml"] +``` diff --git a/marked/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story/raw.md b/marked/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..da1e2216d447a7dd0274c974e4967588d3d0e00e --- /dev/null +++ b/marked/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story/raw.md @@ -0,0 +1,9 @@ +| **Item** | **Details** | +|------------------------------|-------------| +| **Summary** | As a service owner or property manager, I want to issue reboot requests for my API Provider-managed network access devices (such as gateways or mesh controllers) to recover from faulty network states or to perform administrative resets, ensuring reliable connectivity for tenants or guests. | +| **Roles, Actors and Scope** | **Roles:** customer:user
            **Actors:** Service owners, property managers, API providers.
            **Scope:** Trouble to Resolution (T2R) - Issue immediate or scheduled reboot requests for specific devices. Retrieve status of previously created reboot requests. | +| **Pre-conditions** | 1. The API consumer is onboarded and holds credentials with proper scopes (e.g., `reboot-requests:write`, optionally `devices:write`).
            2. The devices are installed and managed by the API provider supporting reboot management. | +| **Begins when** | The API client makes a `POST` request to `/reboot-requests` with a list of device IDs and an optional `atTime` to schedule the reboot. | +| **Ends when** | The reboot is executed by the API Provider-managed device or the request is withdrawn. | +| **Post-conditions** | - The specified device(s) reboot, recovering connectivity or clearing transient faults.
            - System logs are updated to reflect administrative action. | +| **Exceptions** | - `400 Bad Request`: Malformed request body (e.g., invalid time format).
            - `401 Unauthorized`: Access token issues.
            - `403 Forbidden`: Lack of permission for target devices.
            - `404 Not Found`: Specified reboot request or device ID does not exist.| \ No newline at end of file diff --git a/marked/NetworkAccessManagement/documentation/API_documentation/README/raw.md b/marked/NetworkAccessManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f5a82cf57a2e52b761a961409028ccce5b46ec72 --- /dev/null +++ b/marked/NetworkAccessManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1,57 @@ +# CAMARA User Story Guidance + +This document summarizes how to create or modify CAMARA-aligned User Stories using the **Commonalities User Story Template** and how to determine the correct **Scope** value based on the **TM Forum NaaS (TMF 909A)** lifecycle definitions. + +--- + +## 1. Authoritative Sources + +Any information in this guide is derived from the following authoritative sources: + +| Source | Description | Link | +|--------|--------------|------| +| **CAMARA Commonalities – User Story Template** | Canonical template defining fields, structure, and allowed values (Roles, Scope, etc.). | [github.com/camaraproject/Commonalities/documentation/Userstory-template.md](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) | +| **CAMARA Commonalities – Guidelines** | Explains how Commonalities artifacts (User Stories, API Guidelines, etc.) are structured. | [camaraproject.org/commonalities](https://camaraproject.org/commonalities/) | +| **TM Forum TMF 909A – NaaS API Component Suite Profile v1.5** | Defines the lifecycle areas used for the “Scope” field. | [TM Forum TMF 909A – NaaS API Component Suite Profile](https://engage.tmforum.org/HigherLogic/System/DownloadDocumentFile.ashx?DocumentFileKey=70781cfc-1ebb-4ef9-b728-44b34e9c14a1) | +| **TM Forum Open APIs** | APIs referenced for each lifecycle area (TMF 633, 640, 645, 653, 656, 677). | [tmforum.org/open-apis](https://www.tmforum.org/open-apis/) | + +Start with the [CAMARA Commonalities – User Story Template](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) for a comprehensive understanding of user story structure and requirements. From there, you will note a `ReferenceArchitecture` powerpoint is mentioned; this includes slides that summarize the alignment with TM Forum lifecycles, which is further detailed in Section 3 of this document. + +--- + +## 2. User Story Template Overview + +Each CAMARA User Story should include: + +| Field | Description | Guidance | +|-------|--------------|-----------| +| **Title / Summary** | “As a \, I want \ so that \.” | User-centric phrasing. | +| **Roles** | Acceptable values: `customer:user`, `customer:administrator`, `customer:business manager` (from Commonalities template). | Choose based on the actor’s function and access level. | +| **Actor(s)** | Entity or system executing or triggering the story (e.g., API Consumer, API Provider, Service Owner). | Prefer roles over specific implementations. | +| **Scope** | Lifecycle area(s) impacted. See Section 3 below. | Select **one or more** of: Design time, P2O, O2A, U2C, T2R. | +| **Pre-conditions / Begins when** | Required system or business state before the story starts. | Often references catalog or active service. | +| **Steps** | Numbered flow of actions. | Keep technology-neutral. | +| **Post-conditions / Ends when** | Expected outcome or state. | Clarify data, service, or operational result. | +| **Exceptions** | Deviations or failure modes. | Include both business and technical exceptions if relevant. | + +--- + +## 3. Scope Reference (Lifecycle Areas) + +The **Scope** field classifies a user story according to the TM Forum NaaS (TMF 909A) lifecycle model. +Use this section to determine where a story fits. + +| Scope | TM Forum Reference | Summary | Typical APIs / Activities | +|--------|--------------------|----------|----------------------------| +| **Design Time** | TMF 909A § 2.1.5 (Service Catalog) | “Concept-to-Market” activities defining new service specifications. Used for retrieving, creating, or updating service specs prior to runtime. | TMF 633 Service Catalog Management | +| **Prospect to Order (P2O)** | TMF 909A § 2.1.2 | Evaluate what products or services can be offered to a customer. Includes availability checks, feasibility analysis, and resource reservation. | TMF 645 Service Qualification | +| **Order to Activate (O2A)** | TMF 909A § 2.1.1 | Fulfil and activate ordered services, including in-flight modification, suspension, or removal. Covers the operational lifecycle of a service instance. | TMF 640 Activation & Configuration | +| **Usage to Cash (U2C)** | TMF 909A § 2.1.4 | Measure and report service usage for billing or quota management. Includes retrieval, periodic reporting, and threshold notifications. | TMF 677 Usage Consumption | +| **Trouble to Resolution (T2R)** | TMF 909A § 2.1.3 | Monitor, diagnose, and restore services when faults occur. Includes testing, problem creation, updates, and closure. | TMF 656 Service Problem Mgmt, TMF 653 Service Test | + +> **Tip:** +> - If the story involves designing or publishing a service → **Design Time** +> - If it checks availability or feasibility before order → **P2O** +> - If it provisions or modifies active services → **O2A** +> - If it deals with usage or quotas → **U2C** +> - If it handles incidents or assurance → **T2R** diff --git a/marked/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story/raw.md b/marked/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a4016c28831507c522e272f603b6a96ced4e1fa7 --- /dev/null +++ b/marked/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story/raw.md @@ -0,0 +1,10 @@ +| **Item** | **Details** | +|-----------|-------------| +| **Summary** | As a **service owner or API Consumer**, I want to create, modify, and delete **logically isolated network configurations** (Trust Domains) on **API Provider-managed network access devices** (such as gateways or mesh Wi-Fi), defining both network access details and associated policies (such as device limits, bandwidth, or egress rules), so that I can securely segment and govern connectivity for tenants, guests, or IoT devices with predictable behavior and lifecycle control. | +| **Roles, Actors, and Scope** | **Roles:** `customer:user`.
            **Actors:** Service owners, API Consumers, IoT integrators, API providers.
            **Scope:** **Order to Activate (O2A)** — Covers provisioning, modification, and removal of active network configurations. Trust Domain management corresponds to TM Forum **TMF 909A § 2.1.1 “Order to Activate”**, which governs service activation and configuration actions. | +| **Pre-conditions** | 1. The API Consumer has been onboarded with the API provider and obtained valid access credentials with appropriate scopes (e.g., `network-access-management:trust-domains:write`).
            2. The service owner has one or more registered API-provider-managed devices at their premises.
            3. The API provider has implemented the **Network Access Management (NAM)** API supporting Trust Domain configuration. | +| **Begins when** | The API Consumer sends a `POST` request to `/trust-domains` to create a new Trust Domain (optionally including expiration), providing Wi-Fi access details such as SSID, security mode, and credentials, or to `PATCH`/`DELETE` for modification or removal. | +| **Ends when** | The requested Trust Domain is created, updated, or deleted, and the configuration change is successfully reflected on the associated network access devices. | +| **Post-conditions** | - New Trust Domains are provisioned and active on designated or inferred network devices, enforcing logical traffic segmentation.
            - Updated configurations replace previous credentials or policies.
            - Trust Domains that are no longer assigned to any device are automatically removed. | +| **Exceptions** | - **400 Bad Request:** Invalid request parameters (e.g., malformed SSID, unsupported security mode).
            - **401 Unauthorized:** Missing, invalid, or expired access token.
            - **403 Forbidden:** Caller lacks sufficient authorization scope or role.
            - **404 Not Found:** Referenced device or Trust Domain ID does not exist.
            - **409 Conflict:** Attempt to delete a non-removable or in-use Trust Domain. | +| **References** | - [CAMARA Commonalities – User Story Template](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)
            - [TM Forum TMF 909A v1.5 § 2.1.1 – Order to Activate](https://projects.tmforum.org/wiki/display/API/TMF640+Activation+and+Configuration+API+REST+Specification)| diff --git a/marked/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist/raw.md b/marked/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6ee276e8f77d6cd6dae7adb52aa35b721d019aff --- /dev/null +++ b/marked/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist/raw.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for network-access-management 0.1.0-alpha.1 in r1.1. + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:---------------:| +| 1 | API definition | M | M | M | M | Y | [relative link](../../code/API_definitions/network-access-management.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.4 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | N | | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | N | | +| 11 | Change log updated | M | M | M | M | N | [relative link](../../CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166949/NetworkAccessManagement+API+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/NetworkAccessManagement/documentation/SupportingDocuments/README/raw.md b/marked/NetworkAccessManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/NetworkAccessManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/NetworkInsights/README/raw.md b/marked/NetworkInsights/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..70bc424ce286b10273a84d63800b882d28028c82 --- /dev/null +++ b/marked/NetworkInsights/README/raw.md @@ -0,0 +1,44 @@ + + + + + + + + + +# NetworkInsights + +Sandbox API Repository to describe, develop, document, and test the NetworkInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/fQCoBg) + +## Scope + +* Service API(s) “NetworkInsights” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. By providing a holistic view — from infrastructure health to user traffic trends — this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. +* Describe, develop, document, and test the API(s) +* Started: May 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fQCoBg) !! update this link to your minutes archive page using the "Share" link and delete the task + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/NetworkInsights/code/API_definitions/network-health-assessment/raw.md b/marked/NetworkInsights/code/API_definitions/network-health-assessment/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..da9d9f19cdc3c26c7107c084b9c776d8f96d1a4e --- /dev/null +++ b/marked/NetworkInsights/code/API_definitions/network-health-assessment/raw.md @@ -0,0 +1,352 @@ +# network-health-assessment + +```yaml +openapi: 3.0.3 +info: + title: Network Health Assessment + description: | + Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. + It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. + By providing a holistic view — from infrastructure health to user traffic trends — this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. + + # Introduction + This API allows users to query the health score of a specified network, which consists of multiple components including the wireless network, transmission network, and core network. + By calculating the health score for each component and then applying weighted calculations, the API provides a comprehensive health score result for the specified network. + + The health score is a value evaluated by the platform based on the performance/fault indicator status of a specific network module, ranging from 0 to 100. Scores above 90 are considered excellent/healthy, + scores between 60 and 80 indicate varying degrees of issues, and scores below 60 mean the network is basically unable to provide normal services. + A specified network contains different network modules, such as wireless networks, transport networks, and core networks. + The “netType” parameter can be used to query the health assessment of the corresponding network module or the entire network. + The health assessment mechanism periodically evaluates the performance and alarm data of network devices and generates reports. + This API provides the latest report results by default. + + # API functionality + The API provides the following functionality: + - Query the health scores of different network modules in the specified network at the latest point in time. + + # Request Parameters Definition: + * **networkId**: Unique identifier of the Assessment network (UUID format). + * **netType**: Modules within the network. Optional values are: NET (the entire network), NET_WIRELESS (wireless network), NET_TRANSPORT (transport network), NET_CORE (core network). + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkInsights +servers: + - url: "{apiRoot}/network-health-assessment/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Health Assessment + description: Query Network Health Assessment scores for specific network modules. +paths: + /health-scores: + post: + tags: + - Network Health Assessment + summary: Query the latest network health score + description: | + Query the health assessment results of the specified network module at the latest time point. + - Returns the health score (0-100) for the selected network module. + operationId: getHealthScores + security: + - openId: + - network-health-assessment:health-scores:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + type: object + required: + - networkId + - netType + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + netType: + $ref: "#/components/schemas/NetTypeEnum" + examples: + EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + responses: + "200": + description: Health score queried successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/HealthInfo" + examples: + RESPONSE_NET: + $ref: "#/components/examples/RESPONSE_EXAMPLE_NET" + RESPONSE_NET_WIRELESS: + $ref: "#/components/examples/RESPONSE_EXAMPLE_NET_WIRELESS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Correlator string, UUID format recommended but any string matching the pattern can be used + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + maxLength: 256 + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network ID in UUID format (unique identifier of the analyzed network) + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + Score: + title: HealthScore + description: Value of the health score (0-100, higher is better) + type: number + format: double + minimum: 0 + maximum: 100 + example: 94.56 + + HealthInfo: + title: NetworkHealthInfo + description: Network health score information + allOf: + - type: object + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + netType: + $ref: "#/components/schemas/NetTypeEnum" + score: + $ref: "#/components/schemas/Score" + scoringTime: + type: string + format: date-time + maxLength: 64 + description: Latest time point of the health score calculation. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2025-12-01T12:00:00Z" + required: + - networkId + - netType + - score + - scoringTime + + NetTypeEnum: + title: NetworkModuleType + description: Enums of network module types + type: string + enum: + - NET + - NET_WIRELESS + - NET_TRANSPORT + - NET_CORE + example: "NET" + + ErrorInfo: + type: object + description: A structured error response providing details about a failed request, including the HTTP status code, an error code, and a human-readable message + required: + - status + - code + - message + properties: + status: + type: integer + format: int32 + minimum: 100 + maximum: 599 + description: HTTP response status code + code: + type: string + maxLength: 96 + description: A human-readable code to describe the error + message: + type: string + maxLength: 512 + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + examples: + EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + RESPONSE_EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + score: 94.56 + scoringTime: "2025-12-01T12:00:00Z" + RESPONSE_EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + score: 90.12 + scoringTime: "2025-12-01T12:00:00Z" +``` diff --git a/marked/NetworkInsights/code/API_definitions/network-traffic-analysis/raw.md b/marked/NetworkInsights/code/API_definitions/network-traffic-analysis/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..131df84a7723be7e5f1afc9311ea9daf04ef296f --- /dev/null +++ b/marked/NetworkInsights/code/API_definitions/network-traffic-analysis/raw.md @@ -0,0 +1,407 @@ +# network-traffic-analysis + +```yaml +openapi: 3.0.3 +info: + title: Network Traffic Analysis + description: | + Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. + It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. + By providing a holistic view-from infrastructure health to user traffic trends-this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. + + # Introduction + The Network Traffic Analysis API utilizes DPI collection technology to capture communication traffic between all services or terminals within the network. + By correlating service-specific data with devices and port resources, it aggregates and calculates the traffic flow for each service, thereby deriving service-based traffic distribution across the entire network. + This data helps identify high-traffic services and traffic load conditions during different time periods, facilitating the provision of appropriate bandwidth for critical services through slicing technology, ultimately enabling efficient utilization of network resources. + + # API functionality + The API provides the following functionality: + - It allows users to directly query access traffic statistics for all services within a specified time period, including the number of accesses and the cumulative values of uplink and downlink traffic. + + # Request Parameters Definition: + * **networkId**: Unique identifier of the analyzed network (UUID format). + * **timePeriod**: Time range for network analysis (start + end time, RFC 3339 with timezone). + * **frequency**: Analysis granularity (enumeration: 'DAY', 'HOUR'). + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkInsights +servers: + - url: "{apiRoot}/network-traffic-analysis/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Traffic Analysis + description: The API allows API consumers to query 5G traffic statistics information for aggregated network-level data. +paths: + /traffic-analysis: + post: + tags: + - Network Traffic Analysis + summary: Get network traffic analysis + description: | + Query 5G traffic statistics information for aggregated network-level data. + operationId: getTrafficAnalysis + security: + - openId: + - network-traffic-analysis:traffic-analysis:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + type: object + required: + - networkId + - timePeriod + - frequency + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + timePeriod: + $ref: "#/components/schemas/TimePeriod" + frequency: + $ref: "#/components/schemas/Frequency" + examples: + ValidRequest: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + timePeriod: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-07-01T12:00:00Z" + frequency: "DAY" + responses: + "200": + description: Successful response with network traffic analysis data + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficAnalysisResponse' + examples: + Success: + $ref: '#/components/examples/TrafficAnalysisSuccess' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Correlator string, UUID format recommended but any string matching the pattern can be used + type: string + pattern: '^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$' + maxLength: 256 + minLength: 1 + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network ID in UUID format (unique identifier of the analyzed network) + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + TimePeriod: + type: object + description: Time range for network traffic analysis. A period of time defined by a start date and an end date + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-07-01T12:00:00Z" + required: + - startDate + + Frequency: + description: Analysis granularity (time interval for aggregation) + type: string + enum: ["DAY", "HOUR"] + example: "DAY" + + TrafficAnalysisResponse: + type: object + description: Response schema for traffic analysis + required: + - message + - data + properties: + message: + type: string + description: Human-readable status message + example: "Network traffic analysis has been completed" + maxLength: 256 + data: + type: object + description: Traffic analysis data + properties: + records: + type: array + description: Array of traffic records per application + minItems: 1 + maxItems: 1000 + items: + type: object + properties: + app: + type: string + description: Application name + example: "whatsapp" + maxLength: 128 + ipv4Address: + type: string + description: Application server IP ipv4 address + example: "202.112.17.122" + format: ipv4 + maxLength: 15 + description: + type: string + description: Application description + example: "A free cross-platform app for messaging, calls, and media sharing." + maxLength: 512 + accessCount: + type: integer + description: Total number of accesses to the application + minimum: 0 + example: 150 + accessUpFlow: + type: integer + description: Total upstream traffic (bytes) + minimum: 0 + example: 102400 # 100 KB + accessDownFlow: + type: integer + description: Total downstream traffic (bytes) + minimum: 0 + example: 204800 # 200 KB + accessFlow: + type: integer + description: Total traffic (up + down, bytes) + minimum: 0 + example: 307200 # 300 KB + startDate: + type: string + format: date-time + description: Start time of the record interval + example: "2024-06-07T00:00:00Z" + pattern: '^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}:\d{2}(Z|[+-]\d{2}:\d{2})$' + maxLength: 30 + endDate: + type: string + format: date-time + description: End time of the record interval + example: "2024-06-07T23:59:59Z" + pattern: '^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}:\d{2}(Z|[+-]\d{2}:\d{2})$' + maxLength: 30 + accessDate: + type: string + format: date + description: Date of the traffic record (YYYY-MM-DD) + example: "2024-06-07" + pattern: '^\d{4}-\d{2}-\d{2}$' + maxLength: 10 + total: + type: integer + description: Total number of application records + minimum: 0 + example: 22 + + ErrorInfo: + type: object + description: A structured error response providing details about a failed request, including the HTTP status code, an error code, and a human-readable message + required: + - status + - code + - message + properties: + status: + type: integer + format: int32 + description: HTTP response status code + code: + type: string + maxLength: 96 + description: A human-readable code to describe the error + message: + type: string + maxLength: 512 + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + examples: + TrafficAnalysisSuccess: + value: + message: "Network traffic analysis has been completed" + data: + records: + - app: "whatsapp" + ipv4Address: "202.112.17.122" + description: "A free cross-platform app for messaging, calls, and media sharing." + accessCount: 150 + accessUpFlow: 102400 # 100 KB + accessDownFlow: 204800 # 200 KB + accessFlow: 307200 # 300 KB + startDate: "2024-06-07T00:00:00Z" + endDate: "2024-06-07T23:59:59Z" + accessDate: "2024-06-07" + total: 22 +``` diff --git a/marked/NetworkInsights/documentation/API_documentation/NHA_User_Story/raw.md b/marked/NetworkInsights/documentation/API_documentation/NHA_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..093c52f767e1d204dd5ffeeb3441f3f481417942 --- /dev/null +++ b/marked/NetworkInsights/documentation/API_documentation/NHA_User_Story/raw.md @@ -0,0 +1,12 @@ +# Network Health Assessment (NHA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Insights API | +| API summary | **Overview**: For private network monitoring, general users cannot intuitively perceive network performance status or identify performance bottlenecks and faults from complex metrics. Therefore, it is necessary to analyze and integrate raw network and device performance data to achieve monitoring of the entire private network’s status from a higher level.
            **Correlation with network-insight API**: The Network Insights API collects, analyzes, and visualizes network-related data, applying deep analysis and insights to enable private network users to understand what is happening on the network, identify potential issues, and make smarter decisions. Specifically, the Network Health Assessment API is based on a pre-configured service monitoring model (which allows for the selection of modules such as RAN, transport network, and core network, according to service conditions, and sets scoring rules, weights, and severe degradation thresholds for their key alarms and performance indicators to generate a health monitoring model). It performs comprehensive calculations to provide composite score data for each module and the entire private network, presenting private network users with an immediate and intuitive view of the business network status. Additionally, it allows for the retrieval of historical scores, prediction of future network performance trends, and the identification of network bottlenecks and fault location.
            **Network Health Assignment API**: It allows users to directly query the latest health assessment score. Based on the health model, this may include scores for modules such as terminals, RAN, transport network, core network, and MEC, as well as a comprehensive score for all modules.

            Proposed API Definitions
            -Input Parameters:
            structCode: module of Network (net, net_wireless, net_transnet, net_corer)

            -Output Parameters:
            time: The time of the score create.
            valid: The validity of the score.
            value: The score of the health.

            An example: Health assessment relies on performance and alarm data from devices such as terminals, wireless base stations, and core network elements within the private network. The entire data management process can follow the steps below.
            Resource Management: The computing platform needs to maintain information on all device assets within the private network and know which devices are included.
            Performance and Alarm Collection: The computing platform can complete data collection via the device network management platform or by connecting directly to the devices.
            Health Assessment Model Generation: Based on the nature of the private network service, indicators for terminals, base stations, or core network elements can be custom selected, and scoring rules can be set for these indicators.
            Health Assessment Result Generation: Based on the collected data and the calculation model, health assessment score records are generated periodically.
            Health Assessment Result Query: Private network users can query results for the most recent time point at any time.| +| Technical viability | This API requires the completion of device performance and alarm data collection. If collecting via a device management system, the collection protocol can be negotiated independently; if connecting directly to the device, collection via the SNMP protocol can be considered. Regarding the design of the health assessment calculation model, the key is to identify the indicators that best reflect performance and fault status across modules such as terminals, RAN, and core network. Then, based on the private network service type, set the weight and threshold for each indicator, and configure the source of the comparison value (period-over-period, year-over-year, or comparison against a fixed value).| +| Commercial viability | Health assessment is intended for organizations and individuals who need to monitor the status of their private network. It typically serves as a foundational feature for the monitoring dashboards of operators’ private network management platforms, and interfaces can also be opened up for private network users or third-party managed platforms to call for secondary development.| + +## ***Summary*** + +General private network users typically lack professional O&M capabilities and are unable to determine the actual operating status of the private network by directly inspecting devices or interpreting complex metric data provided by management platforms. Therefore, it is necessary to provide a series of higher-level visualization functions to facilitate self-management and self-operations for private network users.
            The Network Health Assessment API provides such capabilities for monitoring personnel, enabling them to perform private network health self-checks based on a preconfigured health assessment calculation model. diff --git a/marked/NetworkInsights/documentation/API_documentation/NTA_User_Story/raw.md b/marked/NetworkInsights/documentation/API_documentation/NTA_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eb2f7ca2c731d66ab4a581bc26b8da433bc871f5 --- /dev/null +++ b/marked/NetworkInsights/documentation/API_documentation/NTA_User_Story/raw.md @@ -0,0 +1,12 @@ +# Network Traffic Analysis (NTA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Insights API | +| API summary | **Overview**: For private network monitoring, general users cannot intuitively perceive network performance status or identify performance bottlenecks and faults from complex metrics. Therefore, it is necessary to analyze and integrate raw network and device performance data to achieve monitoring of the entire private network’s status from a higher level.
            **Correlation with network-insight API**: The Network Insights API collects, analyzes, and visualizes network-related data, applying deep analysis and insights to enable private network users to understand what is happening on the network, identify potential issues, and make smarter decisions. Specifically, the Network Traffic Analysis API utilizes DPI collection technology to capture communication traffic between all services or terminals within the network. By correlating service-specific data with devices and port resources, it aggregates and calculates the traffic flow for each service, thereby deriving service-based traffic distribution across the entire network. This data helps identify high-traffic services and traffic load conditions during different time periods, facilitating the provision of appropriate bandwidth for critical services through slicing technology, ultimately enabling efficient utilization of network resources.
            **Network Traffic Analysis API**: It allows users to directly query access traffic statistics for all services within a specified time period, including the number of accesses and the cumulative values of uplink and downlink traffic.

            Proposed API Definitions
            -Input Parameters:
            startTime: Start time for the analysis in the format 'YYYY-MM-DD HH:mm:ss'.
            endTime: End time for the analysis in the format 'YYYY-MM-DD HH:mm:ss'.
            Domain ID (optional): The platform defines the unique identifier for the service..
            period: Period for the analysis ('DAY', 'HOUR', etc.).
            page: Page number for pagination (optional).
            pageSize: Number of records per page for pagination (optional).

            -Output Parameters:
            app: Application name.
            address: Application address.
            description: Application description.
            accessCount: Access count.
            accessUpFlow: Upstream traffic flow.
            accessDownFlow: Downstream traffic flow.
            accessFlow: Total traffic flow.
            startTime: Start time of the record.
            endTime: End time of the record.
            accessDate: Access date.

            An example: Network traffic analysis relies on switches or UPFs to forward traffic data. The entire data management process can follow these steps:
            Resource Management: The computing platform needs to maintain the private network service classification, as well as the relationship between services and application service addresses.
            Data Collection: Utilizing DPI technology, all traffic data is intercepted via traffic tapping or mirrored ports and pushed to a dedicated data analysis server.
            Data Statistical Analysis: Classify and organize data based on services.
            Traffic Analysis Result Query: Private network users can query traffic analysis data for various services within a specified time period at any time.| +| Technical viability | This API requires the association of service addresses with service definitions. Additionally, it needs to intercept and calculate data for requests and responses accessing various service applications. Since the performance and stability of existing applications must not be impacted, traffic mirroring or optical splitting can be considered for data collection and analysis.| +| Commercial viability | Network traffic analysis is suitable only for organizations and individuals who need to monitor private network traffic distribution. It generally serves as a basic function for the monitoring dashboards of operators’ private network product management platforms, or it can be opened via APIs for private network users or third-party managed platforms to call for secondary development.| + +## ***Summary*** + +In addition to focusing on network performance and faults to ensure network stability, private network users also need to monitor business operation status and identify potential performance bottlenecks. Although the developing network slicing technology provides service assurance for key enterprise services, in practice, network traffic analysis enables private network users to clarify the actual load of various services during different time periods, which is beneficial for accurately determining the upper and lower bandwidth limits required by the services. diff --git a/marked/NetworkInsights/documentation/SupportingDocuments/README/raw.md b/marked/NetworkInsights/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/NetworkInsights/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/NetworkSliceBooking/README/raw.md b/marked/NetworkSliceBooking/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a950bd516264ef0a9ad573a454ed345030895bc4 --- /dev/null +++ b/marked/NetworkSliceBooking/README/raw.md @@ -0,0 +1,56 @@ + + + + + + + + + +# NetworkSliceBooking + +Sandbox API Repository to describe, develop, document, and test the NetworkSliceBooking Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/rDPe) + +## Scope +* Service APIs for “Network Slice Booking” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * reserve, dynamically provisioning, query, dynamically delete a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations. + * manage user subscription to the network slices. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: January 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest pre-release is [r2.1](https://github.com/camaraproject/NetworkSliceBooking/releases/tag/r2.1), with the following API versions: + * **network-slice-booking v0.2.0-rc.1** + [[YAML]](https://github.com/camaraproject/NetworkSliceBooking/blob/r2.1/code/API_definitions/network-slice-booking.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-booking.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-booking.yaml) + * **network-slice-assignment v0.1.0-rc.1** + [[YAML]](https://github.com/camaraproject/NetworkSliceBooking/blob/r2.1/code/API_definitions/network-slice-assignment.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-assignment.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-assignment.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NetworkSliceBooking/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NetworkSliceBooking/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NetworkSliceBooking/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Fridays 16:00 CST / 10:00 CEST + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92204181217?password=7ef83098-28d4-417c-95bc-3f0ab7904c8f) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/NetworkSliceBooking) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/NetworkSliceBooking/code/API_definitions/network-slice-assignment/raw.md b/marked/NetworkSliceBooking/code/API_definitions/network-slice-assignment/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1a3f0d226a94b0f297e023925019a6bf68905f8f --- /dev/null +++ b/marked/NetworkSliceBooking/code/API_definitions/network-slice-assignment/raw.md @@ -0,0 +1,1522 @@ +# network-slice-assignment + +```yaml +openapi: 3.0.3 +info: + title: Network Slice Assignment + description: | + This API enables the assignment and release of the device to an existing network slice, as well as retrieving information about devices assigned to a slice or slices assigned to a device. + + This API works with the Network Slice Booking API, which is responsible for creating and managing network slices. The Network Slice Assignment API allows API consumers to manage user subscription to the network slices. + + # Functionality + The Network Slice Assignment API provides the following functionalities: + - **Assign Device**: Allows the API consumer to assign a device to an existing network slice, ensuring that the number of devices does not exceed the maximum defined in the slice QoS profile. + - **Release Device**: Enables the API consumer to release a device from an existing network slice. + - **Get Assigned Devices**: Retrieves information about devices currently assigned to a specific network slice. + - **Retrieve Slices by Device**: Retrieves the list of network slices to which a specific device is assigned. + + # Terms and Definitions + + * **Notification Sink and Token**: + API consumers can provide a notification sink URL and an optional sink credential when assigning a device to a slice. The notification sink is the URL where the API response will be asynchronously delivered, using the HTTP protocol. The sink credential provides authentication or authorization information necessary to enable delivery of events to the target. + + # Parameters + + * **sliceQosProfile**: A set of quality of service parameters that define the requirements for the network slice. It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + * **sliceId**: A unique identifier for a network slice, obtained from the createSlice operation of the Network Slice Booking API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkSliceBooking +servers: + - url: "{apiRoot}/network-slice-assignment/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Slice Assignment + description: Manage Network Slice Assignment +paths: + /slices/{sliceId}/devices: + post: + tags: + - Network Slice Assignment + summary: Assign a device to a network slice + description: | + Assign a device to an existing network slice. The number of devices assigned to the slice must not exceed the maximum number defined in the slice QoS profile. + - If the assignment operation is successful, the response will indicate the status as `SUCCESS`. + - If the number of devices exceeds the maximum allowed for the slice, the response will indicate the status as `FAILURE` with statusInfo as `MAX_DEVICES_EXCEEDED`. + - If the device is already assigned to the slice, the response will indicate the status as `FAILURE` with statusInfo as `DEVICE_ALREADY_ASSIGNED`. + - If the assignment operation is still in progress, the response will indicate the status as `PENDING`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + operationId: assignDevice + security: + - openId: + - network-slice-assignment:devices:assign + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to assign a device to a network slice + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceInput" + examples: + ASSIGN_DEVICE_INPUT_ALL: + $ref: "#/components/examples/ASSIGN_DEVICE_INPUT_ALL" + ASSIGN_DEVICE_INPUT_NUMBER: + $ref: "#/components/examples/ASSIGN_DEVICE_INPUT_NUMBER" + required: true + callbacks: + networkSliceAssignmentSinkCallback: + "{request.body#/sink}": + post: + tags: + - Network Slice Assignment Callback + summary: Network slice assignment callback + description: Callback for network slice assignment events + operationId: postNetworkSliceAssignmentNotification + requestBody: + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + ASSIGNMENT_COMPLETED_EVENT: + $ref: "#/components/examples/ASSIGNMENT_COMPLETED_EVENT" + ASSIGNMENT_DEVICE_EXCEED_EVENT: + $ref: "#/components/examples/ASSIGNMENT_DEVICE_EXCEED_EVENT" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: The result of the device assignment operation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInfo" + examples: + ASSIGN_DEVICE_SUCCESSFUL: + $ref: "#/components/examples/ASSIGN_DEVICE_SUCCESSFUL" + ASSIGN_DEVICE_FAILURE_EXCEEDED: + $ref: "#/components/examples/ASSIGN_DEVICE_FAILURE_EXCEEDED" + ASSIGN_DEVICE_ALREADY_ASSIGNED: + $ref: "#/components/examples/ASSIGN_DEVICE_ALREADY_ASSIGNED" + ASSIGN_DEVICE_SLICE_NOT_FOUND: + $ref: "#/components/examples/ASSIGN_DEVICE_SLICE_NOT_FOUND" + ASSIGN_DEVICE_UNKNOWN_ERROR: + $ref: "#/components/examples/ASSIGN_DEVICE_UNKNOWN_ERROR" + ASSIGN_DEVICE_PENDING: + $ref: "#/components/examples/ASSIGN_DEVICE_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Network Slice Assignment + summary: Get devices assigned to a network slice + description: | + Get information about devices assigned to an existing network slice. + operationId: getDevices + security: + - openId: + - network-slice-assignment:devices:get + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about active slice + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceDevices" + examples: + GET_DEVICES_SUCCESSFUL: + $ref: "#/components/examples/GET_DEVICES_SUCCESSFUL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + /slices/{sliceId}/release: + post: + tags: + - Network Slice Assignment + summary: Release a device from an existing network slice + description: | + Release a device from an existing network slice. + - If the release operation is successful, the response will indicate the status as `SUCCESS` with statusInfo as `RELEASE_COMPLETED`. + - If the device is not assigned to the slice, the response will indicate the status as `FAILURE` with statusInfo as `DEVICE_ALREADY_RELEASED`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + operationId: releaseDevice + security: + - openId: + - network-slice-assignment:devices:delete + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to release a device from a network slice + content: + application/json: + schema: + $ref: "#/components/schemas/ReleaseDeviceInput" + examples: + RELEASE_DEVICE_INPUT_ALL: + $ref: "#/components/examples/RELEASE_DEVICE_INPUT_ALL" + RELEASE_DEVICE_INPUT_NUMBER: + $ref: "#/components/examples/RELEASE_DEVICE_INPUT_NUMBER" + required: true + responses: + "200": + description: The result of the device release operation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceReleaseInfo" + examples: + RELEASE_DEVICE_SUCCESSFUL: + $ref: "#/components/examples/RELEASE_DEVICE_SUCCESSFUL" + RELEASE_DEVICE_ALREADY_RELEASED: + $ref: "#/components/examples/RELEASE_DEVICE_ALREADY_RELEASED" + RELEASE_DEVICE_SLICE_NOT_FOUND: + $ref: "#/components/examples/RELEASE_DEVICE_SLICE_NOT_FOUND" + RELEASE_DEVICE_UNKNOWN_ERROR: + $ref: "#/components/examples/RELEASE_DEVICE_UNKNOWN_ERROR" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /retrieve-slices: + post: + tags: + - Network Slice Assignment + summary: Retrieve all network slices by device + description: | + Retrieve the list of network slices to which a device is assigned. + operationId: retrieveSlicesByDevice + security: + - openId: + - network-slice-assignment:devices:retrieve + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve slices by device + content: + application/json: + schema: + $ref: "#/components/schemas/Device" + examples: + RETRIEVE_INPUT_PHONENUMBER: + $ref: "#/components/examples/RETRIEVE_INPUT_PHONENUMBER" + required: true + responses: + "200": + description: List of slices the device is assigned + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrievedSlicesOutput" + examples: + RETRIEVE_SUCCESSFUL: + $ref: "#/components/examples/RETRIEVE_SUCCESSFUL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + sliceId: + name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SliceId: + description: Slice ID in UUID format + type: string + format: uuid + DeviceInput: + description: | + Request to add device to a slice + **NOTES:** + - It is the responsibility of the API consumer to ensure that the identifiers they are using are associated with the same device. If unable to do that, only a single identifier SHOULD be provided to the API provider. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API Consumer can provide multiple identifiers to ensure compatibility across different network operators. In this case, the API Provider will use one of the identifiers for the API logic without performing any matching checks among the provided identifiers. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Address" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Address: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Address" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Address" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Address: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ReleaseDeviceInput: + description: Request to release a device from a slice + type: object + properties: + device: + $ref: "#/components/schemas/Device" + required: + - device + DeviceAssignmentInfo: + description: | + Information about the device assignment operation returned in the response. + - If more than one type of device identifier is provided in the request, only one identifier will be returned. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + sliceId: + $ref: "#/components/schemas/SliceId" + status: + $ref: "#/components/schemas/AssignmentStatus" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - sliceId + - status + AssignmentStatus: + description: | + Status of the device assignment operation + * `SUCCESS` - Device is successfully assigned to the slice + * `FAILURE` - Device fail to assign to the slice + * `PENDING` - The assignment operation is still in progress + type: string + enum: + - SUCCESS + - FAILURE + - PENDING + AssignmentStatusInfo: + description: | + Additional information about the assignment status + * `ASSIGNMENT_COMPLETED` - The assignment operation has been completed + * `MAX_DEVICES_EXCEEDED` - The number of devices exceeds the maximum allowed for the slice + * `DEVICE_ALREADY_ASSIGNED` - Device is already assigned to the slice + * `SLICE_NOT_FOUND` - The specified sliceId does not exist + * `ASSIGNMENT_UNKNOWN_ERROR` - The assignment operation failed due to an unknown error + * `VALIDATION_PENDING` - The assignment request is pending for validation and verification + type: string + enum: + - ASSIGNMENT_COMPLETED + - MAX_DEVICES_EXCEEDED + - DEVICE_ALREADY_ASSIGNED + - SLICE_NOT_FOUND + - ASSIGNMENT_UNKNOWN_ERROR + - VALIDATION_PENDING + DeviceReleaseInfo: + description: | + Information about the device release from network slice operation returned in the response. + - If more than one type of device identifier is provided in the request, only one identifier will be returned. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + sliceId: + $ref: "#/components/schemas/SliceId" + status: + $ref: "#/components/schemas/ReleaseStatus" + statusInfo: + $ref: "#/components/schemas/ReleaseStatusInfo" + required: + - sliceId + - status + ReleaseStatus: + description: | + Status of the device release operation + * `SUCCESS` - Device is successfully released from the slice + * `FAILURE` - Device fail to release from the slice + type: string + enum: + - SUCCESS + - FAILURE + ReleaseStatusInfo: + description: | + Additional information about the release status + * `RELEASE_COMPLETED` - The release operation has been completed + * `DEVICE_ALREADY_RELEASED` - Device is already released from the slice + * `SLICE_NOT_FOUND` - The specified sliceId does not exist + * `RELEASE_UNKNOWN_ERROR` - The release operation failed due to an unknown error + type: string + enum: + - RELEASE_COMPLETED + - DEVICE_ALREADY_RELEASED + - SLICE_NOT_FOUND + - RELEASE_UNKNOWN_ERROR + RetrievedSlicesOutput: + description: Response containing slices assigned to a device + type: object + properties: + sliceList: + type: array + items: + $ref: "#/components/schemas/SliceInfo" + minItems: 0 + + SliceDevices: + description: Information about devices assigned to a slice + type: object + properties: + deviceList: + type: array + items: + $ref: "#/components/schemas/Device" + minItems: 0 + sliceInfo: + $ref: "#/components/schemas/SliceInfo" + required: + - deviceList + - sliceInfo + SliceInfo: + description: Slice related information. + allOf: + - $ref: "#/components/schemas/SliceAttributes" + - type: object + properties: + sliceId: + $ref: "#/components/schemas/SliceId" + required: + - sliceId + SliceAttributes: + description: Attributes defining the characteristics of the slice + type: object + properties: + serviceTime: + description: | + serviceTime is a period during which the network slice will be reserved. + It is defined by a start time and an end time. + allOf: + - $ref: "#/components/schemas/TimePeriod" + serviceArea: + description: | + serviceArea is a geographical area where the network slice will be reserved. + It can be defined as a circle or a polygon. + allOf: + - $ref: "#/components/schemas/Area" + sliceQosProfile: + description: | + sliceQosProfile is a set of quality of service parameters that define the requirements for the network slice. + It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + allOf: + - $ref: "#/components/schemas/SliceQosProfile" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - serviceTime + - serviceArea + - sliceQosProfile + + SliceQosProfile: + description: | + Quality of service for the network slice. + It includes a set of predefined network slice performance characteristics. + type: object + properties: + maxNumOfDevices: + description: | + maxNumOfDevices is a maximum number of devices that can be connected to the slice + allOf: + - $ref: "#/components/schemas/NumberOfDevices" + downStreamRatePerDevice: + description: | + downStreamRatePerDevice is the maximum downstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + upStreamRatePerDevice: + description: | + upStreamRatePerDevice is the maximum upstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + downStreamDelayBudget: + description: | + downStreamDelayBudget is the maximum allowable downlink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + upStreamDelayBudget: + description: | + upStreamDelayBudget is the maximum allowable uplink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + + + Duration: + description: Specification of duration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#appendix-A) for duration. + type: object + properties: + value: + description: Length of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + NumberOfDevices: + type: integer + example: 5 + description: Maximum number of devices that is allowed to be connected to the network at any point in time. + + format: int32 + minimum: 1 + maximum: 20 + + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-02T12:00:00Z" + required: + - startDate + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 31.22529 + longitude: 121.48905 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + type: string + description: The type of the event + enum: + - "org.camaraproject.network-slice-assignment.v0.status-changed" + minLength: 25 + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: type + mapping: + org.camaraproject.network-slice-assignment.v0.status-changed: "#/components/schemas/AssignmentDeviceEvent" + + AssignmentDeviceEvent: + description: Event to notify about device assignment status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + description: Event details depending on the event type + allOf: + - $ref: "#/components/schemas/DeviceAssignmentInfo" + required: + - data + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + WARN: This optional field in CloudEvents specification is required in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + NetworkSliceBooking422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - NETWORK_SLICE_BOOKING.RESOURCES_NOT_APPLICABLE + examples: + NETWORK_SLICE_BOOKING_422_RESOURCES_NOT_APPLICABLE: + description: Request cannot be processed due to business logic validation failure, e.g. service area is not supported or resources are insufficient + value: + status: 422 + code: NETWORK_SLICE_BOOKING.RESOURCES_NOT_APPLICABLE + message: The request resources are not applicable for slice creation. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Quota Exceed or Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ASSIGNMENT_COMPLETED_EVENT: + summary: Assignment Completed Event + description: Example of notification event sent when device assignment is completed + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-assignment.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + ASSIGNMENT_DEVICE_EXCEED_EVENT: + summary: Assignment Device Exceed Event + description: Example of notification event sent when device assignment fails due to maximum devices exceeded + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-assignment.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "MAX_DEVICES_EXCEEDED" + ASSIGN_DEVICE_INPUT_ALL: + summary: Assign device - All Identifiers + description: Example of request to assign a device to a network slice using all identifiers + value: + device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + sink: + "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + ASSIGN_DEVICE_INPUT_NUMBER: + summary: Assign device - Phone Number Identifier + description: Example of request to assign a device to a network slice using phone number identifier + value: + device: + phoneNumber: "+123456789" + sink: + "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + ASSIGN_DEVICE_SUCCESSFUL: + summary: Assignment Successful + description: Example of successful response for assigning a device to a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + ASSIGN_DEVICE_FAILURE_EXCEEDED: + summary: Assignment Failure for DeviceNum Exceeded + description: Example of failure response for assigning a device to a network slice request due to maximum devices exceeded + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "MAX_DEVICES_EXCEEDED" + ASSIGN_DEVICE_ALREADY_ASSIGNED: + summary: Assignment Failure for Device Already Assigned + description: Example of failure response for assigning a device to a network slice request due to device already assigned + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "DEVICE_ALREADY_ASSIGNED" + ASSIGN_DEVICE_SLICE_NOT_FOUND: + summary: Assignment Failure for Slice Not Found + description: Example of failure response for assigning a device to a network slice request due to sliceId not found + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "SLICE_NOT_FOUND" + ASSIGN_DEVICE_UNKNOWN_ERROR: + summary: Assignment Failure for Unknown Error + description: Example of failure response for assigning a device to a network slice request due to unknown error + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "ASSIGNMENT_UNKNOWN_ERROR" + ASSIGN_DEVICE_PENDING: + summary: Assignment Pending + description: Example of pending response for assigning a device to a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + RELEASE_DEVICE_INPUT_NUMBER: + summary: Release device - Phone Number Identifier + description: Example of request to assign a device to a network slice using phone number identifier + value: + device: + phoneNumber: "+123456789" + RELEASE_DEVICE_INPUT_ALL: + summary: Release device - All Identifiers + description: Example of request to assign a device to a network slice using all identifiers + value: + device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + RELEASE_DEVICE_SUCCESSFUL: + summary: Release Successful + description: Example of successful response for releasing a device from a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "RELEASE_COMPLETED" + RELEASE_DEVICE_ALREADY_RELEASED: + summary: Release Failure for Device Already Released + description: Example of failure response for releasing a device from a network slice request due to device already not assigned to the slice + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "DEVICE_ALREADY_RELEASED" + RELEASE_DEVICE_SLICE_NOT_FOUND: + summary: Release Failure for Slice Not Found + description: Example of failure response for releasing a device from a network slice request due to sliceId not found + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "SLICE_NOT_FOUND" + RELEASE_DEVICE_UNKNOWN_ERROR: + summary: Release Failure for Unknown Error + description: Example of failure response for releasing a device from a network slice request due to unknown error + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "RELEASE_UNKNOWN_ERROR" + GET_DEVICES_SUCCESSFUL: + summary: Get Devices Successful + description: Example of successful response for getting devices assigned to a network slice request + value: + deviceList: + - device: + phoneNumber: "+123456789" + - device: + phoneNumber: "+987654321" + sliceInfo: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + RETRIEVE_INPUT_PHONENUMBER: + summary: Retrieve Slice Info - Phone Number Identifier + description: Example of request to retrieve network slice info using phone number identifier + value: + device: + phoneNumber: "+123456789" + RETRIEVE_SUCCESSFUL: + summary: Retrieve Slice Info Successful + description: Example of successful response for retrieving network slice info request + value: + sliceList: + - serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" +``` diff --git a/marked/NetworkSliceBooking/code/API_definitions/network-slice-booking/raw.md b/marked/NetworkSliceBooking/code/API_definitions/network-slice-booking/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..56a6a3a56f05902890e27d08f138bbd1ac1658ad --- /dev/null +++ b/marked/NetworkSliceBooking/code/API_definitions/network-slice-booking/raw.md @@ -0,0 +1,1117 @@ +# network-slice-booking + +```yaml +openapi: 3.0.3 +info: + title: Network Slice Booking + description: | + The Network Slice Booking (NSB) API provides programmable interface for developers to reserve a slice resource of a selected area within a period, and manage device access control as needed. + For specific details, please refer to [Network Slice Booking API Design.md](https://github.com/camaraproject/NetworkSliceBooking/blob/main/documentation/API_documentation/Network_Slice_Booking_API_Design.md). + + # Introduction + + This API allows the API consumer to book the availability of a network slice, specifying the service time, service area, and quality of service (QoS) profile. + It checks whether the requested QoS profile can be guaranteed for the indicated time and area, and, if so, it reserves the network slice accordingly, and monitors that the slice delivers the QoS profile. The latter process is known as Service Level Agreement (SLA) monitoring. + + The API consumer can also retrieve information about an existing slice or delete a slice. + + # API functionality + + The API provides the following functionality: + - Create a new network slice, specifying the service time, service area, and QoS profile. + - Retrieve information about an existing slice, including the service time, service area, and QoS profile. + - Delete an existing slice. + + # Request Parameters Definition: + * **serviceTime**: is defined by a start time and an end time, which indicates the period during which the network slice will be reserved. + * **serviceArea**: can be defined as a circle or a polygon, allowing for flexible geographical coverage. + * **sliceQosProfile**: includes parameters such as maximum number of devices, downstream and upstream rate per device, and packet delay budget. + * **sliceId**: is a unique identifier for the network slice, which is returned when a slice is created and used to retrieve or delete the slice later. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Network Slice Booking API does not involve the input and output of user personal data. Therefore, the access to Network Slice Booking API is defined as `Client Credentials - 2-legged`. Please refer to [Identify and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkSliceBooking +servers: + - url: "{apiRoot}/network-slice-booking/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Slice Booking + description: Manage Network Slice Booking +paths: + /slices: + post: + tags: + - Network Slice Booking + summary: Creates a new network slice + description: | + Create a new network slice with the expected service time, service area, and QoS profile. + + NOTES: + - If newtwork slice creation is successful, the API consumer will receive a response with code `201 - Created` and a slice ID. + - If requested service area is not supported, the API consumer will receive a response with code `422 - NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED`. + - If the left resources are not sufficient for the requested slice resources, the API consumer will receive a response with code `422 - NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT`. + operationId: createSlice + security: + - openId: + - network-slice-booking:slices:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new network slice + content: + application/json: + schema: + $ref: "#/components/schemas/SliceAttributes" + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + required: true + callbacks: + networkSliceBookingSinkCallback: + "{request.body#/sink}": + post: + tags: + - Network Slice Booking Callback + summary: Network slice booking callback + description: Callback for network slice booking events + operationId: postNetworkSliceBookingNotification + requestBody: + description: Network slice booking event notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + SLICE_CREATED_EVENT_CIRCLE: + $ref: "#/components/examples/SLICE_CREATED_EVENT_CIRCLE" + SLICE_CREATED_EVENT_POLYGON: + $ref: "#/components/examples/SLICE_CREATED_EVENT_POLYGON" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Slice created successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceInfo" + examples: + RESPONSE_CIRCLE: + $ref: "#/components/examples/RESPONSE_CIRCLE" + RESPONSE_POLYGON: + $ref: "#/components/examples/RESPONSE_POLYGON" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/NetworkSliceBooking422" + "429": + $ref: "#/components/responses/Generic429" + + /slices/{sliceId}: + delete: + tags: + - Network Slice Booking + summary: Delete a network slice + description: | + Release slice resources related to sliceId. + + NOTES: + - The deletion operation takes effect immediately, e.g. if the slice is deleted before the end of the service time, the service will end ahead of the scheduled time. + - If the slice is deleted, the API consumer will not be able to retrieve information about the slice. + - The deletion operation is idempotent, meaning that if the slice is already deleted, the API consumer will receive a response with code `204 - No Content`. + operationId: deleteSlice + security: + - openId: + - network-slice-booking:slices:delete + parameters: + - name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Slice deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Network Slice Booking + summary: Get network slcie booking information + description: | + Querying for network slcie booking resource information details. + + NOTES: + - According to sliceId, the API consumer can retrieve information about an existing slice, including the service time, service area, and QoS profile. + - If the slice is deleted, the API consumer will receive a response with code `404 - Not Found`. + operationId: getSlice + security: + - openId: + - network-slice-booking:slices:get + parameters: + - name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about network slice booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceInfo" + examples: + RESPONSE_CIRCLE: + $ref: "#/components/examples/RESPONSE_CIRCLE" + RESPONSE_POLYGON: + $ref: "#/components/examples/RESPONSE_POLYGON" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + description: Bearer authentication for notifications + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SliceId: + description: Slice ID in UUID format + type: string + format: uuid + SliceInfo: + description: Slice related information. + allOf: + - $ref: "#/components/schemas/SliceAttributes" + - type: object + properties: + sliceId: + $ref: "#/components/schemas/SliceId" + required: + - sliceId + + SliceAttributes: + description: Attributes defining the characteristics of the slice + type: object + properties: + serviceTime: + description: | + serviceTime is a period during which the network slice will be reserved. + It is defined by a start time and an end time. + allOf: + - $ref: "#/components/schemas/TimePeriod" + serviceArea: + description: | + serviceArea is a geographical area where the network slice will be reserved. + It can be defined as a circle or a polygon. + allOf: + - $ref: "#/components/schemas/Area" + sliceQosProfile: + description: | + sliceQosProfile is a set of quality of service parameters that define the requirements for the network slice. + It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + allOf: + - $ref: "#/components/schemas/SliceQosProfile" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - serviceTime + - serviceArea + - sliceQosProfile + + SliceQosProfile: + description: | + Quality of service for the network slice. + It includes a set of predefined network slice performance characteristics. + type: object + properties: + maxNumOfDevices: + description: | + maxNumOfDevices is a maximum number of devices that can be connected to the slice + allOf: + - $ref: "#/components/schemas/NumberOfDevices" + downStreamRatePerDevice: + description: | + downStreamRatePerDevice is the maximum downstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + upStreamRatePerDevice: + description: | + upStreamRatePerDevice is the maximum upstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + downStreamDelayBudget: + description: | + downStreamDelayBudget is the maximum allowable downlink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + upStreamDelayBudget: + description: | + upStreamDelayBudget is the maximum allowable uplink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + + + Duration: + description: Specification of duration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#appendix-A) for duration. + type: object + properties: + value: + description: Length of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + NumberOfDevices: + type: integer + example: 5 + description: Maximum number of devices that is allowed to be connected to the network at any point in time. + + format: int32 + minimum: 1 + maximum: 20 + + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-02T12:00:00Z" + required: + - startDate + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 31.22529 + longitude: 121.48905 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + type: string + description: The type of the event + enum: + - "org.camaraproject.network-slice-booking.v0.status-changed" + minLength: 25 + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: type + mapping: + org.camaraproject.network-slice-booking.v0.status-changed: "#/components/schemas/SliceCreatedEvent" + + SliceCreatedEvent: + description: Event to notify a slice creation status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + description: Event details depending on the event type + allOf: + - $ref: "#/components/schemas/SliceInfo" + required: + - data + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + WARN: This optional field in CloudEvents specification is required in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Specified slice resource is not found based on the sliceId + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + NetworkSliceBooking422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED + - NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT + examples: + NETWORK_SLICE_BOOKING_422_SERVICE_AREA_NOT_SUPPORTED: + description: Business logic exception use when the requested service area is not supported + value: + status: 422 + code: NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED + message: The requested service area is not supported. + NETWORK_SLICE_BOOKING_422_RESOURCES_INSUFFICIENT: + description: Business logic exception use when the left resources are not sufficient for the requested slice resources + value: + status: 422 + code: NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT + message: The left resources are not sufficient for the requested slice resources. + Generic429: + description: Quota Exceed or Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + RETRIEVAL_CIRCLE: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + RETRIEVAL_POLYGON: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + RESPONSE_CIRCLE: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + RESPONSE_POLYGON: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + SLICE_CREATED_EVENT_CIRCLE: + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-booking.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + SLICE_CREATED_EVENT_POLYGON: + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-booking.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" +``` diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..26af4c1ec188c252735a279fcc69c5927d504cd7 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom/raw.md @@ -0,0 +1,13 @@ +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API family owner | China Unicom, China Telecom, Huawei | +| API family supporter | China Mobile, China Unicom, China Telecom, Huawei, TBD | +| API summary | There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.

            Proposed API Definitions
            -Input Parameters:
            Service Time:Start Time ~ End Time
            Service Area:Geographical area (Point, Line, Area)
            Guaranteed terminals:Number of terminals
            SLA Targets:SLA KPIs (such as DL/UL Avg Throughput, Latency)

            -Output Parameters:
            Slice Reservation Result: network slice reservation success (with Slice ID) or failure.

            An example: a developer may use this API to book a network slice with expected service time, expected service area, expected guaranteed numbers of terminals and expected SLA targets for 2 hours to 2 weeks in advance for some scheduled events like a live stream festival scheduled in some place.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| +| YAML code available? | No, needs to be provided in yaml. | +| Validated in lab/productive environments? | Yes, in productive network. | +| Validated with real customers? | Yes | +| Validated with operators? | Yes , 3 operators participated in the evaluations. | +| Others | More details can be refered in PPT. | diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ca3eea17bff37d84bd0c7370302464d03bb1b70e --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story/raw.md @@ -0,0 +1,50 @@ +# Network Slice Assignment (NSA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API summary | **Overview**: There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area.
            **Correlation with network-slice-booking API**: The Network Slice Booking API provides such abilities for OTT developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on. Network Slice Assignment API serves as a key user touchpoint in the network slicing service process, enabling OTT service providers to dynamically and in real-time bind their end-users to the network slices that have successfully reserved.This API accomplishes the final step of transformation from "activating slices for business" to "enabling users to experience slices".
            **Network Slice Assignment API**: It allows developers to assign/release users to/from reserved slices, as well as provides functionalities to query assigned slices through user devices and retrieve the list of users currently assigned to a reserved slice by the slice identifier.

            Proposed API Definitions
            -Input Parameters:
            Device: device identifiers (ipv4Address, ipv6Address, phoneNumber, networkAccessIdentifier)
            SliceId: network slice Identifier

            -Output Parameters:
            Slice Assignment Result: device assigned to network slice success or failure (status and reason).

            An example: An OTT service provider (e.g. a live streaming platform) has completed network slice reservation preparations for an upcoming live streaming event. To ensure a high-quality live streaming experience for users, the following steps need to be completed.
            Reservation Preparation: The OTT service provider (e.g., a live streaming platform) successfully provisions a network slice with high uplink bandwidth and low-latency guarantees in advance for an upcoming "online live streaming event" through the `network-slice-booking` API, obtaining a unique `slice_id`.
            User Trigger: Influencer Companies or studios subscribe to the "Dedicate/Premium Streaming Service" on the live streaming platform.
            API Call: The live streaming app calls the `network-slice-assignment` API in the background to associate the terminal information (e.g., mobile number, IP address) of the influencer company/studio with the previously reserved `slice_id`.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| + +## ***Summary*** + +There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slice Booking API provides such abilities for OTT developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.
            The Network Slice Assignment API then lets them dynamically assign end-users to these reserved slices, delivering the guaranteed experience. It allows developers to assign/release users to/from reserved slices, as well as provides functionalities to query assigned slices through user devices and retrieve the list of users currently assigned to a reserved slice by the slice identifier. + +## ***Scenarios - Assignment Scenario 1*** + +**Operators:** + +Telecom provides Network Slice Assignment API for enterprise customer. Assigning slice resources to end-users enables to provide guaranteed network services. + +**API Consumers:** + +OTT as API consumer. Eg: Tiktok +TitTok can Assign the ordered slice resources for end users by this API, achieving the provision of network guarantee services for its end users + +**API End Users:** + +OTT Customers Eg: Tiktok Influencer Studios + +1. Influencers Companies or Studios may order "Dedicate/Premium Streaming Service" provided by Tiktok. +2. Tiktok then help Influencer Companies on binding their devices into the Slice by calling the Network Slice Assignment APIs. + +## ***Scenarios - Assignment Scenario 2*** + +**Operators:** + +Telecom provides Network Slice Assignment API for enterprise customer. Assigning slice resources to end-users enables to provide guaranteed network services. + +**API Consumers:** + +Enterprises Developer. Eg: TV Station Developer + +1. TV Stations usually have grand TV Live Streaming Business. They need Slice Assurance Services to assure that they have dedicated network resources for their streaming. +2. TV Stations APP developer call Network Slice Assignment API provided by Telecom NaaS Platform/Aggregator Platform directly to make it "Streaming Assurance" function on the APP. + +**API End Users:** + +Video Consumer. Eg: Fans watching the game + +1. Fans watching the game can order "Dedicate/Premium Streaming Service" provided by TV App. +2. Fans watching the game can Enjoy a high-definition and smooth competition experience binding their devices into the Slice by calling the Network Slice Assignment APIs. \ No newline at end of file diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..46864da411b944e85ffd34aebd49fd53394480f6 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story/raw.md @@ -0,0 +1,34 @@ +# Network Slice Booking (NSB) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API summary | There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.

            Proposed API Definitions
            -Input Parameters:
            Service Time:Start Time ~ End Time
            Service Area:Geographical area (Point, Line, Area)
            Guaranteed terminals:Number of terminals
            SLA Targets:SLA KPIs (such as DL/UL Avg Throughput, Latency)

            -Output Parameters:
            Slice Reservation Result: network slice reservation success (with Slice ID) or failure.

            An example: a developer may use this API to book a network slice with expected service time, expected service area, expected guaranteed numbers of terminals and expected SLA targets for 2 hours to 2 weeks in advance for some scheduled events like a live stream festival scheduled in some place.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| + +## ***Summary*** + +There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on. + +## ***Scenarios - Booking Scenario 1*** + +**Operators:** + +Telecom Provide Network Slice Booking API, Providing enterprise customers with the ability to order network slice resources at designated times in designated areas, laying the foundation for subsequent enterprise customer service to end users. + +**API Consumers:** + +OTT as API consumer. Eg: Tiktok +TitTok can order network slicing resources for a specific area at a specific time by this API, These resources lay the foundation for providing network guarantee services to end users in the future. + +## ***Scenarios - Booking Scenario 2*** + +**Operators:** + +Telecom Provide Network Slice Booking API on NaaS Platform or Aggregator Platform + +**API Consumers:** + +Enterprises Developer. Eg: TV Station Developer +TV Stations APP developer call Network Slice Booking API provided by Telecom NaaS Platform/Aggregator Platform directly to order network slice resources for the TV station. It provide a resource foundation for the "Streaming Assurance" function on the APP \ No newline at end of file diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..13eafcafed42e8d914720fb2bce8c4fcfebccc33 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design/raw.md @@ -0,0 +1,80 @@ +# Network Slice Booking API Design + +## **Use Cases** +The business modes of Network Slice Booking can be B2B, B2B2C. + +Note: Currently, we've come across the following business modes, which can be grouped into these 3 in general. If there's any other modes, please do not hesitate to propose. + +**1. Scenario 1 - B2B** + + In brief: toB Enterprise customers come to NaaS Platform, book a slice, telecom operator provide the service. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: Enterprise APP Developer + + End User: toB Enterprise Customer + + Example Use Cases: For enterprise customers, who in the past need to talk to a customer manager, to book a slice service. Now those group of customers may renew, modify, or cancel a slice service within a NaaS Service API call. + + +**2. Scenario 2 - B2B2C** + + In brief: OTT abstract the slice api from NaaS Platform, provide a channel for toC individual customers, to buy a slice from NaaS Plaform. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: APP Developer (eg. OTT) + + Slice Product Provider: APP Developer (eg. OTT) + + End User: toC APP End Users (eg. Individuals / Influencers / Streaming Studios ) + + Example Use Cases: + - OTT call the API from any NaaS Platform, in the way of calling Network Slice Booking API. + - OTT abstract the API, make it a Slice Product, provided to toC customers, who are OTT APP End Users. + - End Users buy the service through the APP. + - OTT transfer the request to NaaS Platform. + - Telecom Operators provide the slice service to End Users directly. + +**3. Scenario3 - B2B2C** + + In brief: OTT buy the slice from NaaS Platform, and resell the slice to toC individual customers. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: APP Developer (eg. OTT) + + API Reseller: APP Developer (eg. OTT) + + End User: toC APP End Users (eg. Individuals / Influencers / Streaming Studios ) + + Example Use Cases: + - OTT book slices from any NaaS Platform, in the way of calling Network Slice Booking API. + - OTT may book a bunch of slices of different time and locations at one time. + - Telecom Operators provide slice service for OTT. + - OTT abstract the API to an APP function, and resell the service to End Users. Resell modes depends on OTT itself. + - End Users buy the service from OTT. + + + +## **API Design** + +Generally: Split the slice reservation function and device access control function + - API 1:Reserve a slice resource + - API 2:Device Access Management / Manage the access control of devices to the slice + - Note: Basically there should be a CRUD for "Reserve a Slice Resource" and a CRUD for "Manage the access control of devices to the slice". + + +**API 1:Reserve a slice resource** + - Function: + - Reserve a slice of one selected period and one selected area. + - Device Access Management may happen at any point in time while the resource is in revered-state and in active-state. + + +**API 2:Device Access Management / Manage the access control of devices to the slice** + - Function: + - Allow API caller manage the access control from devices to the slice. + + + diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..66687326035237f16a7fa119e08259682c13ceef --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist/raw.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for network-slice-assignment v0.1.0-rc.1 in r2.1 + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/network-slice-assignment.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0-rc.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/network-slice-assignment.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory for Network Slicing Assignment](/documentation/API_documentation/NSA_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/535625738/NetworkSliceAssignment+API+description) | | + diff --git a/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist/raw.md b/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..afb8b493fd2d0d55b7d5658c273b4871cc73aca0 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist/raw.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for network-slicing-booking v0.2.0-rc.1 in r2.1 + +| Nr | API release assets | alpha | release-candidate | initial
            public | stable
            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/network-slice-booking.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.2.0-rc.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/network-slice-booking.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory for Network Slicing Booking](/documentation/API_documentation/NSB_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link]( https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166982/NetworkSliceBooking+API+description) | | + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9b793062f4c85a23688fc9cf3702f72c22882f17 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15/raw.md @@ -0,0 +1,40 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-03-15 + +*Friday, March 15th, 2024* + +## Attendees (probably incomplete) + +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ludovic (Orange) +* Gregory Liukumovich (Ericsson) +* Kai Zhang (Huawei) +* Ricardo Serrano (Telefonica) +* Rafal Artych (DT) +* Shilpa (DT) +* Thorsten Lohmar (Ericsson) +* Zohaib Khan (CPaaS) +* Guanyu Zhu (Huawei) +* Tanja de Groot (Nokia) +* Christian (Unknown) +* ... + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* v0.1.0 Release scope & timeline +* AOB + +## Issues relevant for v0.1.0 +* Issue#2 Project Initialization https://github.com/camaraproject/NetworkSliceBooking/issues/2 +* Issue#5 Slice Booking API Introduction Documentation https://github.com/camaraproject/NetworkSliceBooking/issues/5 + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, March 29th, 16:00 CST / 9:30 CET +2. Currently, different projects have different release nums. Should we start with v0.1.0? What's the release planning of CAMARA for 2024? +3. Considering about the API name, easy for developers to understand. \ No newline at end of file diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f1bb9e2cf7cdfee14c492b90f9cbe152eb56d4c1 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10/raw.md @@ -0,0 +1,35 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Hanbai Wang (China Mobile) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Kai Zhang (Huawei) +* Ricardo Serrano (Telefonica) +* Thorsten Lohmar (Ericsson) +* Masaharu Hattori(KDDI) +* Jing Hao(China Unicom) + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Meeting Schedule Adjust + * Meeting Links are adjusted. Including meeting links. Links of S2C, Region User Count, Network Slice API are split into 3 different meeting links as suggested. + * Meeting times are adjusted. Later the Bi-weekly meeting will start from 4pm CST, 10am CEST. +* Issue#22 API Design + * Currently, WG come across 3 modes of business scenarios. WG call for more ideas the API mode. + * Questions toward the business mode work flow, the OTT roles, the Aggregator roles are clear. B2B, B2B2C, B2C are need to be considered. API need to compatible the all the modes. + * The architecture need to be adjusted. Aggregator need to adjust to the layer above the operator. + * Review comments will be resolved later. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, May 24th, 16:00 CST / 10:00 CET diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3b496ae863eae700e561e6773032d381cf995d68 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24/raw.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-24 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ricardo Serrano (Telefonica) +* Steve Vickers (Vodafone) +* Thorsten Lohmar (Ericsson) +* Bart van Kaathoven (Ericsson) +* Veerat (Comviva) +* Vidhi Mehta (Comviva) +* Tanja de Groot (Nokia) +* Zach Callahan () + + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Issue#22 API Design + * For the current architecture part: "NaaS Portal" module is not clear, there are some misunderstandings. + * For the Service API part: questions from participant is clarified and aligned. + * Clarifications on participants questions: + * Arrows marked in camara blue are Service API. Arrows marked in black are other APIs. + * API from both Operator and Aggregator Platform, to Developer are CAMARA service api. + * Below the Operator/Aggregator Platform is transformation function. + * Alignments on the following modifications: + * Use "Operator Platform" to substitute "Operator NaaS Portal" expression. + * Refer to CAMARA slides architecture instead. + * Action points: + * Participant will provide architecture reference link under the PR. Modifications on the graph will start. + * Corresponding modifications towards contexts will be conduct after the graph. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, Jun 22th, 16:00 CST / 10:00 CET \ No newline at end of file diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3b496ae863eae700e561e6773032d381cf995d68 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05/raw.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-24 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ricardo Serrano (Telefonica) +* Steve Vickers (Vodafone) +* Thorsten Lohmar (Ericsson) +* Bart van Kaathoven (Ericsson) +* Veerat (Comviva) +* Vidhi Mehta (Comviva) +* Tanja de Groot (Nokia) +* Zach Callahan () + + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Issue#22 API Design + * For the current architecture part: "NaaS Portal" module is not clear, there are some misunderstandings. + * For the Service API part: questions from participant is clarified and aligned. + * Clarifications on participants questions: + * Arrows marked in camara blue are Service API. Arrows marked in black are other APIs. + * API from both Operator and Aggregator Platform, to Developer are CAMARA service api. + * Below the Operator/Aggregator Platform is transformation function. + * Alignments on the following modifications: + * Use "Operator Platform" to substitute "Operator NaaS Portal" expression. + * Refer to CAMARA slides architecture instead. + * Action points: + * Participant will provide architecture reference link under the PR. Modifications on the graph will start. + * Corresponding modifications towards contexts will be conduct after the graph. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, Jun 22th, 16:00 CST / 10:00 CET \ No newline at end of file diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1c9e56621941e9b30b4734e23755ad98e193f174 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19/raw.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-07-19 + + +*Friday, Jul 19th, 2024* + + +## Attendees +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu(Huawei) +* Thorsten Lohmar (Ericsson) +* Tanja de Groot (Nokia) +* Masaharu Hattori(KDDI) +* Bart van Kaathoven(Ericsson) +* Pedro Bento() + + +## Agenda +* Issue#33 and PR#32 API Yaml update +* Issue#38 discussion - Add an “Area” data-type into CAMARA_common.yaml +* Issue#39 discussion - API BACKLOG - Dedicated Networks: Scope Enhancement proposal +* AOB + + +## Issues Discussions +* Issue#33 and PR#32 API Yaml update + * Still modify the yaml file based on previous meeting discussion and It's not finished yet . +* Issue#38 discussion - Add an “Area” data-type into CAMARA_common.yaml + * “Area” data-type for CAMARA_common is not ready for Commnonalities now. + * NSB will refer to the "Area" data-type from device-locaction project before Commnonalities definition + * NSB will follow the update of Commnonalities about “Area” data-type for CAMARA_common. + + +* Issue#39 discussion - API BACKLOG - Dedicated Networks: Scope Enhancement proposal + * Thorsten introduced Dedicated Network API proposal, which aims to provide a highly abstract NaaS API which can support both FBB and MBB scenarios. Thorsten introded the differences between Dedicated Network API with QoD, Site To Cloud VPN, and NSB, which are included in the Proposal PDF. + * Shuting comment that it's a great proposal for long term plan. There are different ways of the slice/vpn/leased line compositions regarding on AN, TN, CN respectively. "Dedicated Networks" needs time to really support all ways of network compositions. From commercial side, it also needs to think about the product setting problem, especially when it comes to price. Eg. In terms of TN, OTN is far more expensive than IP. + * It will take some time to discuss the proposals in the Issue#39 + + +## AOB +1. The next call will be on Friday, 2nd Aug, 16:00 CST / 10:00 CET + + + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9ec902edccda98cb39832a05d41460e109163042 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23/raw.md @@ -0,0 +1,34 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-05-23 + + +*Friday, May 23rd, 2025* + + +## Attendees +* Dongrui Xiao (China Unicom) +* Xunli Yang (Huawei) +* Rafal Artych (DT) +* Masaharu Hattori(KDDI) + + +## Agenda +* Issue#46 discussion - prepare for the version release, update the API Yaml +* PR#20 update - API Design documentation update +* AOB + + +## Issues Discussions +* Issue#46 discussion + * Still modify the yaml file, change api version to 0.1.0-alpha.1 and prepare for the version release. + * Update the test case files. + * +* PR#20 update - API Design documentation update + * The remaining PR#20 has been discussed well. + * NSB will update the API Design documentation and continuously modify it following the Commnonalities. + + +## AOB +1. The next call will be on Friday, 6th June, 16:00 CST / 10:00 CET + + + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e19772e502c9288b83f377970e65361bc43cc828 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06/raw.md @@ -0,0 +1,39 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-06-06 + + +*Friday, June 6th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Rafal Artych (DT) +* Surajj Jaggernath (Vodafone) +* Vidhi Mehta () + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* Issue#54 discussion - prepare for the version release, update the API Yaml +* Issue#51 discussion - prepare API test cases +* AOB + + +## Issues Discussions +* Issue#54 discussion - prepare for the version release, update the API Yaml + * Some error code has been refined, and discuss the description. + * Modify the yaml file, Remove 401 AUTHENTICATION_REQUIRED error code according to camaraproject/Commonalities#429. + * +* Issue#51 discussion - prepare API test cases + * Modify API test cases based on yaml changes. + +## Timeline +* Need to follow up with CAMARA release management. +* Pre-release with API release candidate version need to prepared and released +* Create release PR for delivering the release version r1.1 for Fall25 M3 milestone -June 21st + +## AOB +1. The next call will be on Friday, 20th June, 16:00 CST / 10:00 CET + + + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7c8739ebcea500617e4814b963519f79a41740a4 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04/raw.md @@ -0,0 +1,41 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-07-04 + + +*Friday, July 4th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Rafal Artych (DT) +* Masaharu Hattori (KDDI) +* Veerat Kulkarni + + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* PR#59 discussion - add some developer-friendly API description, make some general terminology adjustments. +* Free discussion +* AOB + + +## Issues Discussions +* PR#59 discussion + * Add some developer-friendly API description in yaml file. + * Unified the terminology for the defined QoSProfile parameters to align with QoD. + * Ready for the API release-candidate version. +* Free discussion - Business Model for Sclice Booking + * If there is a new infrastructure needs to be spawned up for the specific network slice booking instance, what is the price model for the specific slice? + * Action: This issue can be further discussed in detail after the meeting through email or issue channels. + +## Timeline +* Need to follow up with CAMARA release management. +* Merge PR#54, and release API release candidate version r1.1. + +## AOB +1. The next call will be on Friday, 18th July, 16:00 CST / 10:00 CET + + + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..246629441f2bde510edbbcb671c98336a7f2f163 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18/raw.md @@ -0,0 +1,50 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-07-18 + + +*Friday, July 18th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Masaharu Hattori (KDDI) +* Surajj Jaggernath (Vodafone) + + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* Issue#63 discussion - Naming pattern correction. +* Issue#64 discussion - Supplemental description fields for the API endpoints. +* Issue#65 discussion - Modify the name for schema QosProfile to avoid confusions. +* Free discussion +* AOB + + +## Issues Discussions +* Issue#63 discussion + * Property and similar names should follow lowerCamelCase naming pattern + * Schema names follow UpperCamelCase naming pattern +* Issue#64 discussion + * Post: Add description field to help the developers understand the endpoint API better. + * Delete: Ideally this should have some explanation about delete usage e.g. what is the effect of deleting the session befor the endtime that is was booked for, etc. + * Get: The description may contain more details about the provided resource information that is returned when calling this end-point. +* Issue#65 discussion +* Modify the name for schema QosProfile to avoid confusions. + * There is already a definition for QosProfile within the API qos-profiles in QualityOnDemand which is different from the definition here (as defined as profile for one device). + * Consider to modify the name for the profile which is specific for NetworkSliceBooking to avoid confusions. + * Action: decided on the name `SliceQosProfile`. +* Free discussion + * The plan for the API of managing device access. + * Plan to release this part of API in the next release(Spring26). + +## Timeline +* Need to follow up with CAMARA release management. +* Merge PR#54, and release API release candidate version r1.1. + +## AOB +1. The next call will be on Friday, 1st Aug, 16:00 CST / 10:00 CET + + + diff --git a/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26/raw.md b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..80a4dc352a9ab7039cf9c5bad21408e76ee7c3b0 --- /dev/null +++ b/marked/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26/raw.md @@ -0,0 +1,46 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-09-26 + + +*Friday, Sep 26th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Rafal Artych (DT) + + +## Agenda +* The API is about to be released(Thanks for everyone's great work!) +* Discuss the plan for the next version in Spring26: + * Issue#81 discussion - [Generic422 error rename to be more explicit](https://github.com/camaraproject/NetworkSliceBooking/issues/81). + * Issue#82 discussion - [Add tests for polygon area validation limits (between 3-15 points)](https://github.com/camaraproject/NetworkSliceBooking/issues/82). + * Issue#83 discussion - [Add corresponding tests on x-correlator parameters](https://github.com/camaraproject/NetworkSliceBooking/issues/83). + * Issue#84 discussion - [Add asynchronous callback in the createSession operation](https://github.com/camaraproject/NetworkSliceBooking/issues/84). +* Free discussion +* AOB + + +## Issues Discussions +* Meta-release Fall25 + * Network-slice-booking v0.1.0 is about to be released in Fall25. + * Keep an eye on the possible release schedule for future versions, ref:[Proposal to Adopt a Dual-Phase Meta-Release Cadence for CAMARA APIs #194](https://github.com/camaraproject/Governance/issues/194) +* Issue#81 discussion + * Split the 422 error with "service area is not supported" error and "resources are insufficient" error. + * Optional change: + * `NetworkSliceBooking422` -> `SERVICEAREA_NOT_SUPPORTED` for "service area is not supported" error. + * `NetworkSliceBooking422` -> `RESOURCES_INSUFFICIENT` for "resources are insufficient" error. +* Issue#82 discussion + * Add tests for polygon area validation limits (between 3-15 points). +* Issue#83 discussion + * Add corresponding tests on x-correlator parameters + * To be clarified: whether to add schenarios for inconsistent x-correlator in request and response. +* Issue#84 discussion + * Plan to add asynchronous callback in the next release. + * To be discussed: notification API. +* Free discussion + * Plan to release this part of API in the next release(Spring26). + + +## AOB +1. The next call will be on Friday, 10th Oct, 16:00 CST / 10:00 CET diff --git a/marked/NumberRecycling/README/raw.md b/marked/NumberRecycling/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eebbc061c49149d48dea5212f54dd025564d46a9 --- /dev/null +++ b/marked/NumberRecycling/README/raw.md @@ -0,0 +1,51 @@ + + + + + + + + + +# NumberRecycling + +Sandbox API Repository to describe, develop, document, and test the NumberRecycling API within the [Know Your Customer (KYC)](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ggCaBQ) + +## Scope + +* Service API “NumberRecycling” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API consumer with the ability to: + * Check whether the subscriber of the phone number has changed. A common scenario is when Application service provider (ASP) wants to check whether there has been a change in the user associated with the phone number after the specified date. This allows the ASP to ensure that a phone number is correctly linked to an user and prevent the mis-delivery of SMS messages. +* Describe, develop, document, and test the API +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/NumberRecycling/releases/tag/r2.2) (Fall25), with the following API versions: + * **number-recycling v0.2.0** + [[YAML]](https://github.com/camaraproject/NumberRecycling/blob/r2.2/code/API_definitions/number-recycling.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NumberRecycling/r2.2/code/API_definitions/number-recycling.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NumberRecycling/r2.2/code/API_definitions/number-recycling.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NumberRecycling/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NumberRecycling/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NumberRecycling/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of KnowYourCustomer Sub Project are held virtually + * Schedule: Bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Minutes: Access [meeting minutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/NumberRecycling/code/API_definitions/number-recycling/raw.md b/marked/NumberRecycling/code/API_definitions/number-recycling/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a87a922d1c9ba0817ff58565719ed2334037eaf0 --- /dev/null +++ b/marked/NumberRecycling/code/API_definitions/number-recycling/raw.md @@ -0,0 +1,355 @@ +# number-recycling + +```yaml +openapi: 3.0.3 +info: + title: Number Recycling + description: | + The API can be used to check whether the subscriber of the phone number has changed. + A common scenario is when Application service provider (ASP) wants to check whether there has been a change in the user associated with the phone number after the specified date. This allows the ASP to ensure that a phone number is correctly linked to an user and prevent the mis-delivery of SMS messages. + + For example, below is a potential scenarios: + * Scenario 1 + * Pre-conditions + * User A signed a contract with MNO A for the phone number '+123456789' on October 9, 2023, and is still using it. + * User A also signed contracts with ASP A on December 22, 2023 for its services. + * ASP A holds the contract date (2023-12-22) and the phone number (+123456789) for User A. + * Currently, on November 2, 2024, ASP A wishes to send a SMS message to User A. + * Potential operations + * ASP A sends a request with specified date (2023-12-22) and phone number (+123456789) to the Number Recycling API. + * The API response sets to 'false', indicating that there has not been a change in the user associated with the phone number. + * Post-conditions + * ASP A decides to send the SMS message to User A. + * By following these steps, ASP A ensures that a phone number is linked to User A. + + Number_Recycling_scenario_1 + + Note: + * When API receives a request with specified date on which a user signed a contract with MNO, the API respond sets to 'false'(e.g., 2023-10-09 in the Scenario 1 of the figure above). + + * Scenario 2 + * Pre-conditions + * User A signed a contract with MNO A for the phone number '+123456789' on October 9, 2023, and canceled it on February 25, 2024. Subsequently, User B signed a contract with MNO A for the same phone number on September 21, 2024, and is still using it. + * User A also signed contracts with ASP A on December 22, 2023 for its services. + * ASP A holds the contract date (2023-12-22) and the phone number (+123456789) for User A. + * Currently, on November 2, 2024, ASP A wishes to send a SMS message to User A. + * Potential operations + * ASP A sends a request with specified date (2023-12-22) and phone number (+123456789) to the Number Recycling API. + * The API response sets to 'true', indicating that there has been a change in the user associated with the phone number. + * Post-conditions + * ASP A decides to stop sending the SMS message to User A and contacts User A by mail. + * By following these steps, ASP A ensures that a phone number is not linked to User A and prevents the mis-delivery of the SMS message. + + Number_Recycling_scenario_2 + + Note: + * When the API receives a request with specified date during which there is no contract with MNO for the phone number, the API respond sets to 'true'(e.g., the period between 2024-02-25 and 2024-09-20 in the Scenario 2 of the figure above). + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: tbd + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/NumberRecycling +servers: + - url: '{apiRoot}/number-recycling/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /check: + post: + security: + - openId: + - number-recycling:check + tags: + - Check Number Recycling + summary: Check whether the subscriber of the phone number has changed. + description: Check whether the subscriber of the phone number has changed. + operationId: checkNumberRecycling + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Check whether the subscriber of the phone number has changed. + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCheckNumRecycling' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CheckNumRecyclingInfo" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/Generic422' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + CreateCheckNumRecycling: + type: object + required: + - specifiedDate + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + specifiedDate: + type: string + format: date + description: Specified date to check whether there has been a change in the subscriber associated with the specific phone number, in RFC 3339 calendar date format (YYYY-MM-DD). + example: "2024-10-31" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + CheckNumRecyclingInfo: + type: object + required: + - phoneNumberRecycled + properties: + phoneNumberRecycled: + type: boolean + description: | + Set to true (Boolean, not string) when there has been a change in the subscriber associated with the specific phone number after “specifiedDate”. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + responses: + Generic200: + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/CheckNumRecyclingInfo' + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + InvalidArgument: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + OutOfRange: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permission Denied: + description: Permission denied. OAuth2 token access not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + Phone Number Used By Different Network Operator: + description: Provided phone number is used by a different network operator + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Device Not Applicable: + description: Service not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number + Unnecessary Identifier: + description: An explicit identifier is provided when a phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified +``` diff --git a/marked/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story/raw.md b/marked/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7d1a252830864b728c0aae885ba755060cec74e7 --- /dev/null +++ b/marked/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story/raw.md @@ -0,0 +1,11 @@ +# Number Recycling API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check whether there has been a change in the user associated with the phone number after the specified date so that I can ensure that a phone number is correctly linked to an user and prevent mis-delivery before sending SMS messages to an user. | +| ***Roles, Actors and Scope*** | **Actors:** Application service providers (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Communication service Provider (CSP), Channel Partner.
            **Scope:** Checks whether there has been a change in the user associated with the specific phone number after the specified date. | +| ***Pre-conditions*** |The preconditions are listed below:
            1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform optionally through a Channel Partner.
            2. The ASP:BusinessManager has successfully subscribed to the Number Recycling API product from the product catalog optionally through a Channel Partner.
            3. The ASP:Administrator has onboarded the ASP:User to the platform.| +| ***Activities/Steps*** | **Starts when:** The ASP application makes a POST request to the Number Recycling API, including specified date and the phone number provided by the user in the ASP:User. This request could be done via (or not) the Channel Partner.
              **Ends when:** The CSP's Number Recycling Server responds to confirm if the user associated with the phone number has changed since the specified date. | +| ***Post-conditions*** | The ASP:User could continue offering to send the SMS messages to the user associated with the phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Recycling API operations.
              - Unauthorized: Not valid credentials (e.g., use of already expired access token).
              - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| diff --git a/marked/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist/raw.md b/marked/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..02d7bcb7a4120e823b92a05dc1ea576c639ca895 --- /dev/null +++ b/marked/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for number-recycling v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
              public | stable
              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/number-recycling.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Number_Recycling_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/number-recycling.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/0AFmBQ) | diff --git a/marked/NumberRecycling/documentation/SupportingDocuments/README/raw.md b/marked/NumberRecycling/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/NumberRecycling/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/NumberVerification/README/raw.md b/marked/NumberVerification/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..515bcfb5a36ec8a835ae227a694a20a067d366c4 --- /dev/null +++ b/marked/NumberVerification/README/raw.md @@ -0,0 +1,55 @@ + + + + + + + + + +# NumberVerification + +Incubating API Repository to evolve and maintain the definitions and documentation of the NumberVerification Service API within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XzTe) + +## Scope + +* Service API for “NumberVerification” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * verify the phone number associated with the SIM used in the device connected to the mobile data network. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 +* Incubating stage since: February 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/NumberVerification/releases/tag/r3.2) (Fall25), with the following API versions: + * **number-verification v2.1.0** + [[YAML]](https://github.com/camaraproject/NumberVerification/blob/r3.2/code/API_definitions/number-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NumberVerification/r3.2/code/API_definitions/number-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NumberVerification/r3.2/code/API_definitions/number-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NumberVerification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NumberVerification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NumberVerification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564484/Minutes+-+Number+Insights) +* Mailing list: + * To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . + * A message to all Contributors of this Sub Project can be sent using . +* [Slack channel](https://app.slack.com/client/T05S5J43YQP/C062DDGR60L) diff --git a/marked/NumberVerification/code/API_definitions/number-verification/raw.md b/marked/NumberVerification/code/API_definitions/number-verification/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..38cad6b99867914c82af5cd4518fe6a2b1aea6ae --- /dev/null +++ b/marked/NumberVerification/code/API_definitions/number-verification/raw.md @@ -0,0 +1,324 @@ +# number-verification + +```yaml +openapi: 3.0.3 +info: + title: Number Verification + description: | + This API can verify or retrieve the **mobile phone number** that is currently allocated by the network operator to the SIM in the end user's device + + In this API **phone number** refers to the mobile phone number. + + # Introduction + + The Number Verification API is used by the API consumer to perform real-time checks to verify the phone number of a mobile device being used to access the application. This check can be done either by the API provider, returning "true" or "false", or by the application, by matching the phone number returned by the API Provider with the phone number of the device that is being used. + + It uses silent authentication (Network-based authentication or SIM-Based authentication) to verify possession of a phone number in the background without requiring user interaction. There are neither one-time passwords (OTP) received by SMS nor authenticator app downloads, so it is much simpler. It can be used at sign up, login, or transaction time to validate that a user's SIM is not spoofed or cloned. + + # Relevant Definitions and Concepts + + - **Network-Based Authentication**: Authentication mechanism based on the identification of the mobile phone. + A network operator knows to which subscriber a connected mobile phone belongs and what its associated phone number is. + - **SIM-Based Authentication**: Authentication mechanism based on the identification of the subscriber's SIM installed in the user's device. This mechanism relies on temporary tokens provided by the operator, as defined by [GSMA TS.43](https://www.gsma.com/newsroom/gsma_resources/ts-43-service-entitlement-configuration/) and [GSMA ASAC](https://www.gsma.com/newsroom/gsma_resources/asac-01-v1-0/). + + # API Functionality + + This API enables an API Consumer to verify or retrieve the phone number of the mobile device being used to access their service. + + # The Authentication Request + + **For NumberVerification the API provider guarantees that there is no user interaction.** Would user interaction be needed the authorization server returns an error. + Authentication methods such as SMS OTP or user/password are incompatible, as the goal is to validate the mobile phone number that is accessing the App. + + ## Authentication Request with a temporary token + + If the API Consumer has a TS.43 temporary token created on the mobile device then this API works over all connections e.g. WiFi taking advantage of the SIM-Based authentication. + The API Consumer sends the temporary token to their backend which either: + - Sends a CIBA Authentication Request, as described in the current release [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement), with a parameter `login_hint=operatortoken:`. + - Or sends a JWT-Bearer token request as described in [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement), with the TS.43 token in the `sub` claim of the JWT assertion with the format `"operatortoken:"`. + + How the API Consumers get a TS.43 temporary token and how this token is sent to their backend, is out-of-scope of the API definition. + + ## Authentication Request without a temporary token + + If the API Consumer does not have a TS.43 temporary token then the API Consumer must use OpenId Connect Authorization Code Flow as described in the current release of [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement). + For this method of authentication to work, the device must be connected to the mobile network. + + The API Consumer should use the request parameter prompt=none in the Authentication Request, as described in **[OIDC Connect](https://openid.net/specs/openid-connect-core-1_0.html#AuthRequest)**, ensuring no user interaction. + The API Provider implies the request parameter prompt=none in the Authentication Request for this API. + + # Resources and Operations overview + + This API currently provides two endpoints which both require a **3-legged token** obtained by using one of the two methods indicated in _The Authentication Request_ section. This therefore **excludes** using, for example, SMS/OTP or user/password as an authentication method: + - The /verify endpoint checks whether the mobile phone number registered by the user with the API consumer matches the one actually associated with the mobile device. + It can receive either a hashed or a plain text phone number as input. + It compares the received phone number with the user's phone number associated to the access token in order to respond **true/false**. + - The /device-phone-number endpoint returns the phone number associated by the network operator with the SIM in the end user's device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to [Identity and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + In the case of the Number Verification API scenario and according to the API definition, 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This must be done via mobile network authentication. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NumberVerification +servers: + - url: '{apiRoot}/number-verification/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath +tags: + - name: Phone number verify + description: API operation to verify a phone number received as input. It can be received either in plain text or hashed format. + - name: Phone number share + description: API operation to return the phone number associated to the access token. +paths: + /verify: + post: + tags: + - Phone number verify + summary: Verifies if the received hashed/plain text phone number matches the phone number associated with the access token + description: | + Verifies if the specified phone number (either in plain text or hashed format) matches the one that the user is currently using. Only one of the plain or hashed formats must be provided. + - The number verification will be done for the user that has authenticated via mobile network + - It returns true/false depending on if the hashed phone number received as input matches the authenticated user's `device phone number` associated to the access token + operationId: phoneNumberVerify + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationRequestBody' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationMatchResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/PhoneNumberVerificationPermissionDenied403' + security: + - openId: + - number-verification:verify + /device-phone-number: + get: + tags: + - Phone number share + summary: Returns the phone number associated with the access token + description: | + Returns the phone number so the API clients can verify the number themselves: + - It will be done for the user that has authenticated via mobile network + - It returns the authenticated user's `device phone number` associated to the access token + operationId: phoneNumberShare + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationShareResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/PhoneNumberVerificationPermissionDenied403' + security: + - openId: + - number-verification:device-phone-number:read +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + NumberVerificationRequestBody: + type: object + description: Payload to verify the phone number. + minProperties: 1 + maxProperties: 1 + properties: + phoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + hashedPhoneNumber: + description: Hashed phone number. SHA-256 (in hexadecimal representation) of the mobile phone number in **E.164 format (starting with country code)**. Prefixed with '+'. + type: string + pattern: '^[a-fA-F0-9]{64}$' + example: 32f67ab4e4312618b09cd23ed8ce41b13e095fe52b73b2e8da8ef49830e50dba + NumberVerificationMatchResponse: + type: object + description: Number verification result + required: + - devicePhoneNumberVerified + properties: + devicePhoneNumberVerified: + $ref: '#/components/schemas/DevicePhoneNumberVerified' + NumberVerificationShareResponse: + type: object + description: Number verification share result + required: + - devicePhoneNumber + properties: + devicePhoneNumber: + $ref: '#/components/schemas/DevicePhoneNumber' + DevicePhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + DevicePhoneNumberVerified: + description: Number verification. True, if it matches + type: boolean + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + example: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + PhoneNumberVerificationPermissionDenied403: + description: | + Client does not have sufficient permission. + In addition to regular scenario of `PERMISSION_DENIED`, other scenarios may exist: + - Client authentication was not via mobile network. In order to check the authentication method, AMR parameter value in the 3-legged user's access token can be used and make sure that the authentication was not either by SMS+OTP nor username/password (`{"code": "NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK","message": "Client must authenticate via the mobile network to use this service"}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK: + value: + status: 403 + code: NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK + message: Client must authenticate via the mobile network to use this service +``` diff --git a/marked/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story/raw.md b/marked/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc5bfb0608ef82f9f4668442ff091f95c6a3fbcf --- /dev/null +++ b/marked/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story/raw.md @@ -0,0 +1,10 @@ +# Number Verification Share Device Phone Number API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want to retrieve the phone number associated with a mobile connection from which the API call was made, so that I can ensure that I obtain the correct phone number and avoid fraud e.g. identity theft. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
              **Scope:**
              -Returns the phone number associated with the access token so the ASPs can get the phone number and verify it themselves.| +| ***Pre-conditions*** |The preconditions are listed below:
              1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
              2. The ASP:BusinessManager has successfully subscribed to the Number Verification product from the CSP's product catalog via (or not) a Channel Partner.
              3. The ASP:Administrator has onboarded the ASP:User to the CSP API platform via (or not) a Channel Partner.
              4. The ASP:User performs an authorization request to CSP.
              5. The CSP checks access & End-User approval then provide access token to the ASP:User
              6. The ASP:User get the access token, via (or not) the Channel Partner, based on network authentication to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the number verification API. This request could be done via (or not) the Channel Partner.
                **Ends when:** The CSP's Number Verification Server answers providing the phone number corresponding to the one of the end-user's device from which the request was triggered. The ASP:User can check if this number corresponds to the one keyed by the End-User. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the End-User phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Verification API operations
                - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                - Not able to provide: Client authentication was not performed via mobile network or temporary token. Not working on mobile hotspot (tethering) neither Wifi nor VPN mobile connections **if client authentication is performed via mobile network** | \ No newline at end of file diff --git a/marked/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story/raw.md b/marked/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d4008e0e19fe298e33b93f13ac1a8a1759ea82e3 --- /dev/null +++ b/marked/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story/raw.md @@ -0,0 +1,10 @@ +# Number Verification Verify API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want to verify the phone number associated with a mobile connection so I can validate the phone number identity that a end-user introduces in my application during a registration process.| +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                **Scope:**
                - Verifies if the specified phone number (plain text or hashed format) matches the one that the user is currently using. | +| ***Pre-conditions*** |The preconditions are listed below:
                1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                2. The ASP:BusinessManager has successfully subscribed to the Number Verification product from the CSP's product catalog via (or not) a Channel Partner.
                3. The ASP:Administrator has onboarded the ASP:User to the CSP API platform via (or not) a Channel Partner.
                4. The ASP:User performs an authorization request to CSP.
                5. The CSP checks access & End-User approval then provide access token to the ASP:User
                6. The ASP:User get the access token, via (or not) the Channel Partner, based on network authentication to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the number verification API providing in the request the phone number provided by the End-User on the ASP:User. This request could be done via (or not) the Channel Partner. This input could be hashed or plain.
                  **Ends when:** The CSP's Number Verification Server responds to confirm whether the provided phone number matches the end-user's device from which the request was initiated or not. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the user phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Verification API operations
                  - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                  - Invalid input: Not valid input data to invoke operation (e.g. phone number without the '+' prefix).
                  - Not able to provide: Client authentication was not performed via mobile network or temporary token. Not working on mobile hotspot (tethering) neither Wifi nor VPN mobile connections **if client authentication is performed via mobile network** | \ No newline at end of file diff --git a/marked/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist/raw.md b/marked/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3cbe1d140e629082b0ee36aaf870cf6bb3674b2e --- /dev/null +++ b/marked/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist/raw.md @@ -0,0 +1,32 @@ +# API Readiness Checklist + +Checklist for number-verification v2.1.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                  initial | public-release
                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/number-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/number-verification.yaml) | +| 6 | User stories | O | O | O | M | Y | [get](/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md) [verify](/documentation/API_documentation/NumberVerification_verify_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [get](/code/Test_definitions/number-verification-phoneNumberShare.feature) [verify](/code/Test_definitions/number-verification-phoneNumberVerify.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [get](/code/Test_definitions/number-verification-phoneNumberShare.feature) [verify](/code/Test_definitions/number-verification-phoneNumberVerify.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue[#216](https://github.com/camaraproject/NumberVerification/issues/216) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | Y | [link](https://www.open-gateway.com/operators-map) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81134263/NumberVerification+API+description) | + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..af6513d76499de5c8bfcf60eb7a1e12e47daaba9 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8947512beb2c8f0978e308ddc6d2fb68172ccbc9 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md @@ -0,0 +1,101 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >discussion continued on Thursday 15th Dec'22 + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                  Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                  + +### NumberVerify + +#### Recommendation: + + >Enable Number Verify API with two flavors: + - Based on dedicated endpoint (Orange + TEF proposal) + - Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design. +In the second case, this particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - work with 2 yaml files with API description. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..71f6f1fab2049df975d4a7668bfabfc1bd014e4a --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md @@ -0,0 +1,49 @@ +# Week 14 meeting + +## Participants + +4th April 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|JORGE GARCIA HOSPITAL|Telefonica| +|5|PEDRO ANTONIO DE ALARCON SANCHEZ|Telefonica| +|6|Ludovic ROBERT|Orange| +|7|Cormac Hegarty|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- [Issue #16](https://github.com/camaraproject/SimSwap/issues/16) +- participants discussed a scenario, when Service Provider requests sim swap information from MNO, but MNO has not registered an event of a sim Change. MNO performed API service, but value cannot be returned. Success (200OK) or Error (401 or 404) has implications for API consumer. We continue discusson to find a solution that can be described in API documentation. +- + +### NumberVerify + +- [Issue #35](https://github.com/camaraproject/NumberVerification/issues/35) +- participants identified that current API descriptions might be confusing for software developers - two API definitions: MobileConnect & Camara flavors +- Mobile Identity APIs are commercially available and software developers are familiar with existing API design - making a change to existing standard might not be identified by software developers community as a positive change, due to existing Mobile Connect implementations +- additionally, recent changes inside commonalities working group describing the [notation of APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md#42-inputoutput-resource-definition), requires adoption of Mobile Connect API definition to be compliant with CAMARA +- there is a willingness to assess benefits developers can get when having APIs fully compliant to MC but not same from one implementation to another . + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion on next alignment call that takes place 13th April 2023. diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e8f6f8cccd7405c5255bf635d6a3d64f1e1ded07 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..45341e3ba91317308c5807d9f3a2fe8da281f1da --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cda161c9585539791c3632a5d201527c62ae43e0 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9ae7482fe5a6934e8bddb25795b9035d5fee0a03 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..68518c789d2a536584063bd84f254404532609dd --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delivered + +### NumberVerify + +- CAMARA & MC APIs yaml files delivered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..22155de9cf8fb5d93e47c0611b518c0b58800fc9 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..313a13075ee7a176dddcaa6188022fad0cdfbe2f --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..63405e4d97b2ee52df13e8d99f7ffdcac17fe96b --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e255de039e1896635c5ee155c9e954694e8449ed --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md @@ -0,0 +1,65 @@ +# Week 40 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1ae1221bfd38f71d6d01facc3fb1d25853123373 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f99cf3cffeb305aa4df198b476dd7a51917332ea --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9d9df6609c0c1b5dcacf2c626ccb3c475a4c8aa9 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..501c50c324316b15642af656e03999e08cca9058 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc346b5fddbbc2c9802739dffca35566e6b015ba --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..91bb132a9aa939faff9886f81057301aa8b34993 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB + +* discussion about MWC 2024 +* add commits to sub-projects for next release + +## APs diff --git a/marked/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a679824263eaab80ea5f81ba640492098b11118b --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/marked/NumberVerification/documentation/MeetingMinutes/README/raw.md b/marked/NumberVerification/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..dd06842f8da1c28a43f771c23c1147eea6fa92a9 --- /dev/null +++ b/marked/NumberVerification/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [Number Verification Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/NumberVerification) diff --git a/marked/OTPValidation/README/raw.md b/marked/OTPValidation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..de4315d57af18d299201a9011fb5947b9106b818 --- /dev/null +++ b/marked/OTPValidation/README/raw.md @@ -0,0 +1,64 @@ + + + + + + + + + +# OTPValidation + +Incubating API Repository to evolve and maintain the definitions and documentation of OTPValidation Service API within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/yDXe) + +## Scope + +* Service APIs for “OTPValidation” (see APIBacklog.md) + * The OTP SMS API facilitates real-time verification of a user's device by sending a unique code via SMS to the specified mobile phone number. The process involves three key steps: +1. **Code Generation and Delivery:** + The send-code operation is used by the API consumer (e.g., an application) to request a one-time code to be sent by SMS to the application user's mobile phone along with an message to the user's mobile device. +2. **User Input:** + The user receives the SMS and enters the received code into the application. +3. **Verification:** + The application submits the entered code using the validate-code operation, which then verifies its accuracy and responds with a confirmation indicating whether the code is valid. + +This process ensures secure, real-time validation of user possession of the specified device, enhancing authentication security. + * by delivering a one-time password (OTP) to it through SMS and validating the received code with the user's operator after the code is entered as requested. + * Started: October 2022 + * Incubating stage since: February 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/OTPValidation/releases/tag/r3.2) (Fall25), with the following API versions: + * **one-time-password-sms v1.1.1** + [[YAML]](https://github.com/camaraproject/OTPValidation/blob/r3.2/code/API_definitions/one-time-password-sms.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/OTPValidation/r3.2/code/API_definitions/one-time-password-sms.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/OTPValidation/r3.2/code/API_definitions/one-time-password-sms.yaml) +* The latest public release is always available here: https://github.com/camaraproject/OTPValidation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/OTPValidation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/OTPValidation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564484/Minutes+-+Number+Insights) +* Mailing list + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . + + + diff --git a/marked/OTPValidation/code/API_definitions/one-time-password-sms/raw.md b/marked/OTPValidation/code/API_definitions/one-time-password-sms/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8c53b624df350ea503e4ecd9fab863be0c5d7a14 --- /dev/null +++ b/marked/OTPValidation/code/API_definitions/one-time-password-sms/raw.md @@ -0,0 +1,449 @@ +# one-time-password-sms + +```yaml +openapi: 3.0.3 +info: + title: One Time Password SMS + description: |- + Service API to send short-lived OTPs (one time passwords) to a phone number via SMS and validate it afterwards, in order to verify the phone number as a proof of possession. + + # Relevant Definitions and concepts + - **OTP**: *One Time password* is a one-time authorization code that is valid for only one login session or transaction. + + # API Functionality + It enables a Service Provider (SP) to send an OTP code by SMS and validate it to verify the phone number (MSISDN) as a proof of possession. + + # Resources and Operations overview + This API currently provides two endpoints, one to send an OTP to a given phone number and another to validate the code received as input. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/OTPValidation +servers: + - url: "{apiRoot}/one-time-password-sms/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: OTP Management + description: API operations to manage OTP codes +paths: + /send-code: + post: + tags: + - OTP Management + summary: Sends a message including an OTP code to the given phone number + description: |- + Sends an SMS with the desired message and an OTP code to the received phone number. + operationId: sendCode + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/SendCodeBody' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/SendCodeResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/SendCodeForbiddenError403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - one-time-password-sms:send-validate + /validate-code: + post: + tags: + - OTP Management + summary: Verifies the OTP received as input + description: |- + Verifies the code is valid for the received authenticationId + operationId: validateCode + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/ValidateCodeBody' + required: true + responses: + '204': + description: The OTP was successfully validated + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/ValidateCodeBadRequestError400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - one-time-password-sms:send-validate +components: + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SendCodeBody: + description: Structure to request sending a code to a phone number + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + message: + $ref: '#/components/schemas/Message' + required: + - message + - phoneNumber + SendCodeResponse: + description: Structure to provide authentication identifier + type: object + properties: + authenticationId: + $ref: '#/components/schemas/AuthenticationId' + required: + - authenticationId + ValidateCodeBody: + description: Strcuture to request code verification + type: object + properties: + authenticationId: + $ref: '#/components/schemas/AuthenticationId' + code: + $ref: '#/components/schemas/Code' + required: + - authenticationId + - code + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+346661113334' + Message: + type: string + description: Message template used to compose the content of the SMS sent to the phone number. It must include the following label indicating where to include the short code `{{code}}` + pattern: .*\{\{code\}\}.* + maxLength: 160 + example: '{{code}} is your short code to authenticate with Cool App via SMS' + AuthenticationId: + type: string + description: unique id of the verification attempt the code belongs to. + maxLength: 36 + example: ea0840f3-3663-4149-bd10-c7c6b8912105 + Code: + type: string + description: temporal, short code to be validated + maxLength: 10 + example: AJY3 + ErrorInfo: + description: Structure to describe error + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + ValidateCodeBadRequestError400: + description: |- + Problem with the client request. In addition to regular scenario of `INVALID_ARGUMENT`, another scenarios may exist: + - Too many unsuccessful attempts (`{"code": "ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED","message": "The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP"}`) + - Expired authenticationId (`{"code": "ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED","message": "The authenticationId is no longer valid"}`) + - OTP is not valid for the provided authenticationId (`{"code": "ONE_TIME_PASSWORD_SMS.INVALID_OTP","message": "The provided OTP is not valid for this authenticationId"}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED + - ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED + - ONE_TIME_PASSWORD_SMS.INVALID_OTP + examples: + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + OTP_VALIDATION_400_VERIFICATION_FAILED: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED + message: The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP + OTP_VALIDATION_400_VERIFICATION_EXPIRED: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED + message: The authenticationId is no longer valid + OTP_VALIDATION_400_INVALID_OTP: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.INVALID_OTP + message: The provided OTP is not valid for this authenticationId + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SendCodeForbiddenError403: + description: |- + Client does not have sufficient permissions to perform this action. + In addition to regular scenario of `PERMISSION_DENIED`, another scenarios may exist: + - Too many code requests were sent (`{"code": "ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED","message": "Too many OTPs have been requested for this MSISDN. Try later."}`) + - The given phoneNumber can't receive an SMS due to business reasons in the operator, e.g. fraud, receiving SMS is not supported, etc (`{"code": "ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED","message": "Phone_number can't receive an SMS due to business reasons in the operator."}`) + - The given phoneNumber is blocked to receive SMS due to any blocking business reason in the operator (`{"code": "ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED","message": "Phone_number is blocked to receive SMS due to any blocking business reason in the operator."}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED + - ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED + - ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED + examples: + GENERIC_403_PERMISSION_DENIED: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + OTP_VALIDATION_403_MAX_OTP_CODES_EXCEEDED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED + message: Too many OTPs have been requested for this MSISDN. Try later. + OTP_VALIDATION_403_PHONE_NUMBER_NOT_ALLOWED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED + message: Phone_number can't receive an SMS due to business reasons in the operator. + OTP_VALIDATION_403_PHONE_NUMBER_BLOCKED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED + message: Phone_number is blocked to receive SMS due to any blocking business reason in the operator. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic429: + description: Either out of resource quota or reaching rate limiting + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. +``` diff --git a/marked/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story/raw.md b/marked/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..be54f15c7e5f044b3e05e399605baccd1f8dc30c --- /dev/null +++ b/marked/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story/raw.md @@ -0,0 +1,27 @@ +# OTPVAlidationAPI API User Story + +OTP Validation user story is splitted in 2 steps. Both steps are mandatory to perform this user story. + + +## Step 1 - Request to send a code + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the phone number associated with the line from which the call was made, so I can get a proof of possession of the phone number. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User, Customer:BusinessManager, Customer:Administrator
                  **Actors:** Application service providers, hyperscalers, application developers, end users, Communication service Provider (CSP).
                  **Scope:**
                  - Customer:User asks CSP to send a message featuring a 'code' variable via SMS. The message is specified by Customer:User. In the API response a request identifier is provided to link with validation step. | +| ***Pre-conditions*** |The preconditions are listed below:
                  1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                  2. The Customer:BusinessManager has successfully subscribed to the OTP Validation API product from the product catalog.
                  3. The Customer:Administrator has onboarded the Customer:User to the platform.
                  4. The Customer:User performs an authorization request to CSP
                  5. The Customer:user has the access token allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The customer application makes a POST send-code via the OTPValidation API providing in the request the phone number keyed by the user on the application and a message to be displayed in the SMS. This message must indicate where the code must be indicated (like _"Your code to validate your onboarding for niceApp is {code}"_).
                    **Ends when:** The CSP OTP Validation server performs two operations: 1/answers to the API request providing a request identifier (authenticationId), and 2/send the SMS to the line identified by provided phone number. | +| ***Post-conditions*** | The customer application has a request identifier (authenticationId) and will be able to validate code keyed by the end user. | +| ***Exceptions*** | Several exceptions might occur during the OTP Validation API operations
                    - Unauthorized: Not valid credentials.
                    - Invalid input: Not valid input data to invoke operation (e.g. phone number without the '+' prefix).
                    - Permission denied: Too any request to send code for a phone number in a short time.
                    - Permission denied: phone number not able to receive SMS.| + + +## Step 2 - Validate a code + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the phone number associated with the line from which the call was made, so I can get a proof of possession of the phone number. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User, Customer:BusinessManager, Customer:Administrator
                    **Actors:** Application service providers, hyperscalers, application developers, end users, Communication service Provider (CSP).
                    **Scope:**
                    - Following a send code request, Customer:User asks end user to keyed the code received by SMS. Then Customer:User sends this code to the CSP to validate that the code matches the one send by the CSP in the SMS. | +| ***Pre-conditions*** |The preconditions are listed below:
                    1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                    2. The Customer:BusinessManager has successfully subscribed to the OTP Validation API product from the product catalog.
                    3. The Customer:Administrator has onboarded the Customer:User to the platform.
                    4. The Customer:User performs an authorization request to CSP
                    5. The Customer:User has the access token allowing a secure access of the API.
                    6. The Customer:User has performed a valid send-code previously and has the request identifier (authenticationId).
                    7. The end user received via a SMS a code and keyed it on the application. | +| ***Activities/Steps*** | **Starts when:** The Customer-User makes a POST validate-code via the OTPValidation API providing in the request the code keyed by the end user on the application and the authenticationId obtained in the response of the send-code step. .
                      **Ends when:** The CSP OTP Validation server check the code and answers 204 if the code matches else an exception is sent. | +| ***Post-conditions*** | The customer application could continue offering its service to the end user with the confirmation of the end user phone number. | +| ***Exceptions*** | Several exceptions might occur during the OTP Validation API operations
                      - Unauthorized: Not valid credentials.
                      - Invalid input: Not valid input data to invoke operation (e.g. code not provided).
                      - Invalid input: The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP
                      - Invalid input:The provided OTP is not valid for this authenticationId
                      - Invalid input:The authenticationId is no longer valid| diff --git a/marked/OTPValidation/documentation/API_documentation/OTP_SMS_API/raw.md b/marked/OTPValidation/documentation/API_documentation/OTP_SMS_API/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4c8691c6e882bba1cedb342dcfef966aae910690 --- /dev/null +++ b/marked/OTPValidation/documentation/API_documentation/OTP_SMS_API/raw.md @@ -0,0 +1,147 @@ +# Overview + +One Time Password SMS API is used to send short-lived OTPs (one time passwords) to a phone number via SMS and validate it afterwards, in order to provide a proof of possession of the phone number. + +## 1\. Introduction + +One Time Password SMS API performs real-time checks to verify that the user possessed the device that carries the indicated mobile phone number. It provides a frequent method of verifying possession of the device by delivering an OTP (one-time password) through SMS and validating it afterwards. + +SMS OTP (one time password) is a secure method for providing one-time access to an application or performing a single transaction. OTP is most effective and legitimate for a single transaction, unlike user-generated passwords. It is a secure authentication method where a text containing a unique alphanumeric or numeric code is sent to a mobile number (MSISDM). + +The recipient then uses this code or password as an additional layer of security to login to a service, website or app. + + +## 2\. Quick Start + +The usage of the API is based on several resources. + +Before starting to use the API, the developer needs to know about the below specified details: + +**API service endpoint** + +Two endpoints are defined in One Time Password SMS API:
                      +- POST /one-time-password-sms/v0/send-code : Sends an SMS with the desired message and an OTP code to the received phone number +- POST /one-time-password-sms/v0/validate-code : Verifies the received code as input is valid for the given authenticationId. + +**Authentication** + +Security access token based on two-legged authentication is required for this API with dedicated scope. + +Sample API invocations are presented in Section 4.6. + +## 3\. Authentication and Authorization + +One Time Password SMS API uses OAUTH 2.0 client credentials grant which is applicable for server to server use cases involving trusted partners or clients without any protected user data involved. [[1]](#1) + +## 4\. API Documentation + +### 4.1 API Version + +0.1.0 + +### 4.2 Details + +#### 4.2.1 Endpoint Definition + +Following table defines API endpoints of exposed REST based for One Time Password SMS API operations. + +| **Endpoint** | **Operation** | **Description** | +| -------- | --------- | ----------- | +| POST /one-time-password-sms/v0/send-code | **Request to send an OTP code** | Create request in order to send an OTP code with the given message to a mobile phone number | +| POST /one-time-password-sms/v0/validate-code | **Request to validate an OTP code** | Create a request to validate an OTP code for the given authenticationId | + + +#### One Time Password SMS API Resource Operations: +
                      + +| **Request code** | +| -------------------------- | +| **HTTP Request**
                      POST /one-time-password-sms/v0/send-code
                      **Query Parameters**
                      No query parameters are defined.
                      **Path Parameters**
                      No path parameters are defined.
                      **Request Body Parameters**
                      **phoneNumber**: A phone number belonging to the user. 'E164 with +' format.
                      **message**: Message template used to compose the content of the SMS sent to the phone number. It must include the following label indicating where to include the short code `{{code}}`. + +
                      **Response**
                      **200: OK**
                      Response body:
                      **authenticationId** : Unique id of the verification attempt the code belongs to.
                      **400:** **INVALID_ARGUMENT**
                      **401:** **UNAUTHENTICATED**
                      **403:** **PERMISSION_DENIED**
                      **403:** **ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED**
                      **403:** **ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED**
                      **403:** **ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED**
                      **404:** **NOT_FOUND**
                      **405:** **METHOD_NOT_ALLOWED**
                      **406:** **NOT_ACCEPTABLE**
                      **415:** **UNSUPPORTED_MEDIA_TYPE**
                      **429:** **TOO_MANY_REQUESTS**
                      **500:** **INTERNAL**
                      **503:** **UNAVAILABLE**
                      **504:** **TIMEOUT**
                      +
                      + +
                      + +| **Validate code** | +| -------------------------- | +| **HTTP Request**
                      POST /one-time-password-sms/v0/validate-code
                      **Query Parameters**
                      No query parameters are defined.
                      **Path Parameters**
                      No path parameters are defined.
                      **Request Body Parameters**
                      **authenticationId**: Unique id of the verification attempt the code belongs to.
                      **code**: Temporal, short code to be validated. + +
                      **Response**
                      **204: The OTP was successfully validated**
                      **400:** **INVALID_ARGUMENT**
                      **400:** **ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED**
                      **400:** **ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED**
                      **400:** **ONE_TIME_PASSWORD_SMS.INVALID_OTP**
                      **401:** **UNAUTHENTICATED**
                      **403:** **PERMISSION_DENIED**
                      **404:** **NOT_FOUND**
                      **405:** **METHOD_NOT_ALLOWED**
                      **406:** **NOT_ACCEPTABLE**
                      **415:** **UNSUPPORTED_MEDIA_TYPE**
                      **429:** **TOO_MANY_REQUESTS**
                      **500:** **INTERNAL**
                      **503:** **UNAVAILABLE**
                      **504:** **TIMEOUT**
                      +
                      + +
                      + +### 4.3 Errors + +Since CAMARA One Time Password SMS API is based on REST design principles and blueprints, well defined HTTP status codes and families specified by community are followed [[2]](#2). + +Details of HTTP based error/exception codes for One Time Password SMS API are described in Section 4.2 of each API REST based method. +Following table provides an overview of common error names, codes, and messages applicable to One Time Password SMS API. + +| No | Error Name | Error Code | Error Message | +| --- | ---------- | ---------- | ------------- | +|1 |400 | INVALID_ARGUMENT | "Client specified an invalid argument, request body or query param" | +|2 |400 | ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED | "The authenticationId is no longer valid" | +|3 |400 | ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED | "The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP" | +|4 |400 | ONE_TIME_PASSWORD_SMS.INVALID_OTP | "The provided OTP is not valid for this authenticationId" | +|5 |401 | UNAUTHENTICATED | "Request not authenticated due to missing, invalid, or expired credentials" | +|6 |403 | PERMISSION_DENIED | "Client does not have sufficient permissions to perform this action" | +|7 |403 | ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED | "Too many OTPs have been requested for this MSISDN. Try later." | +|8 |403 | ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED | "Phone_number can't receive an SMS due to business reasons in the operator" | +|9 |403 | ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED | "Phone_number is blocked to receive SMS due to any blocking business reason in the operator" | +|10 |404 | NOT_FOUND | "A specified resource is not found" | +|11 |405 | METHOD_NOT_ALLOWED | "The requested method is not allowed/supported on the target resource" | +|12 |406 | NOT_ACCEPTABLE | "The server can't produce a response matching the content requested by the client through Accept-* headers" | +|13 |415 | UNSUPPORTED_MEDIA_TYPE | "The server refuses to accept the request because the payload format is in an unsupported format" | +|14 |429 | TOO_MANY_REQUESTS | "Either out of resource quota or reaching rate limiting" | +|15 |500 | INTERNAL | "Server error" | +|16 |503 | UNAVAILABLE | "Service unavailable" | +|17 |504 | TIMEOUT | "Request timeout exceeded. Try later." | + +
                      + +### 4.4 Policies + +N/A +
                      + +### 4.5 Code Snippets +
                      +Snippets elaborates REST based API call with "*curl"* to request + + +Please note, the credentials for API authentication purposes need to be adjusted based on target security system configuration. + +| Snippet 1. Request code | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/one-time-password-sms/v0/send-code`
                      -H 'accept: application/json'
                      -H 'Content-Type: application/json'
                      -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
                      -d '{ "phoneNumber": "+346661113334",
                      "message": "{{code}} is your short code to authenticate with Cool App via SMS"}' | +| The response will be:
                      200
                      -d '{ "authenticationId": "ea0840f3-3663-4149-bd10-c7c6b8912105" }'| +
                      + +| Snippet 2. Validate code | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/one-time-password-sms/v0/validate-code`
                      -H 'accept: application/json'
                      -H 'Content-Type: application/json'
                      -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
                      -d '{ "authenticationId": "ea0840f3-3663-4149-bd10-c7c6b8912105",
                      "code": "AJY3"}' | +| The response will be:
                      204 | +
                      + + + +### 4.6 FAQs + +(FAQs will be added in a later version of the documentation) + +### 4.7 Terms + +N/A + +### 4.8 Release Notes + +N/A + + +## References + + +[1] [CAMARA Commonalities : Authentication and Authorization Concept for Service APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Working/CAMARA-AuthN-AuthZ-Concept.md)
                      +
                      [2] [HTTP Status codes spec](https://restfulapi.net/http-status-codes/)
                      diff --git a/marked/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist/raw.md b/marked/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a06b37b0f69f007c42e817f8e7ceabb1fd3ddcb0 --- /dev/null +++ b/marked/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist/raw.md @@ -0,0 +1,34 @@ +# API Readiness Checklist + +Checklist for one-time-password-sms v1.1.1 in r3.2 + + +| Nr | API release assets | alpha | release-candidate | public-release
                      initial | public-release
                      stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/one-time-password-sms.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v1.1.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/one-time-password-sms.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/OTPValidationAPI_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [send code](/code/Test_definitions/one-time-password-sms-sendCode.feature) / [validate code](/code/Test_definitions/one-time-password-sms-validateCode.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [send code](/code/Test_definitions/one-time-password-sms-sendCode.feature) / [validate code](/code/Test_definitions/one-time-password-sms-validateCode.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue [#120](https://github.com/camaraproject/OTPValidation/issues/120) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101463/OTPValidation+API+description) | + + +(1) The certified company(s) can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + + + + + + diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..af6513d76499de5c8bfcf60eb7a1e12e47daaba9 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8947512beb2c8f0978e308ddc6d2fb68172ccbc9 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md @@ -0,0 +1,101 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >discussion continued on Thursday 15th Dec'22 + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                      Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                      + +### NumberVerify + +#### Recommendation: + + >Enable Number Verify API with two flavors: + - Based on dedicated endpoint (Orange + TEF proposal) + - Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design. +In the second case, this particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - work with 2 yaml files with API description. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0a79887c49c1f3cfaa0d0437587b8e10e4a74417 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls/raw.md @@ -0,0 +1,49 @@ +# Week 14 meeting + +## Participants + +4th April 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|JORGE GARCIA HOSPITAL|Telefonica| +|5|PEDRO ANTONIO DE ALARCON SANCHEZ|Telefonica| +|6|Ludovic ROBERT|Orange| +|7|Cormac Hegarty|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- [Issue #16](https://github.com/camaraproject/SimSwap/issues/16) +- participants discussed a scenario, when Service Provider requests sim swap information from MNO, but MNO has not registered an event of a sim Change. MNO performed API service, but value cannot be returned. Success (200OK) or Error (401 or 404) has implications for API consumer. We continue discusson to find a solution that can be described in API documentation. +- + +### NumberVerify + +- [Issue #35](https://github.com/camaraproject/NumberVerification/issues/35) +- participants identified that current API descriptions might be confusing for software developers - two API definitions: MobileConnect & Camara flavors +- Mobile Identity APIs are commercially available and software developers are familiar with existing API design - making a change to existing standard might not be identified by software developers community as a positive change, due to existing Mobile Connect implementations +- additionally, recent changes inside commonalities working group describing the [notation of APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md#42-inputoutput-resource-definition), requires adoption of Mobile Connect API definition to be compliant with CAMARA +- there is a willingness to assess benefits developers can get when having APIs fully compliant to MC but not same from one implementation to another. + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion on next alignment call that takes place 13th April 2023. diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e8f6f8cccd7405c5255bf635d6a3d64f1e1ded07 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..45341e3ba91317308c5807d9f3a2fe8da281f1da --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cda161c9585539791c3632a5d201527c62ae43e0 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9ae7482fe5a6934e8bddb25795b9035d5fee0a03 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..29874d2ccd614c3d792135d738ac2c191bee7c4e --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls/raw.md @@ -0,0 +1,47 @@ +Hmmm# Week 28 meeting + +## Participants + +13th July 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..68518c789d2a536584063bd84f254404532609dd --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delivered + +### NumberVerify + +- CAMARA & MC APIs yaml files delivered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..22155de9cf8fb5d93e47c0611b518c0b58800fc9 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..313a13075ee7a176dddcaa6188022fad0cdfbe2f --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..63405e4d97b2ee52df13e8d99f7ffdcac17fe96b --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..323c0698a349ea2e2f89c473656b43224bc73938 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md @@ -0,0 +1,65 @@ +# Week 38 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1ae1221bfd38f71d6d01facc3fb1d25853123373 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f99cf3cffeb305aa4df198b476dd7a51917332ea --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9d9df6609c0c1b5dcacf2c626ccb3c475a4c8aa9 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..501c50c324316b15642af656e03999e08cca9058 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc346b5fddbbc2c9802739dffca35566e6b015ba --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8cf16b0524f70768844adcaa0d742cc655d2225d --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md @@ -0,0 +1,40 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB +* discussion about MWC 2024 +* add commits to sub-projects for next release +## APs diff --git a/marked/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a679824263eaab80ea5f81ba640492098b11118b --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/marked/OTPValidation/documentation/MeetingMinutes/README/raw.md b/marked/OTPValidation/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7ecd3d05464c0c68c0ec28b3168e09afa3909905 --- /dev/null +++ b/marked/OTPValidation/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [OTP Validation Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/OTP+Validation) \ No newline at end of file diff --git a/marked/OTPValidation/documentation/SupportingDocuments/README/raw.md b/marked/OTPValidation/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..220f01caa5a015a6cfd54e60ac74769669ec4546 --- /dev/null +++ b/marked/OTPValidation/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/marked/OptimalEdgeDiscovery/README/raw.md b/marked/OptimalEdgeDiscovery/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..83cc4b4abe5899dfa1c8e7e39347152bb0fc6925 --- /dev/null +++ b/marked/OptimalEdgeDiscovery/README/raw.md @@ -0,0 +1,53 @@ +
                      + + + + + + + + +# OptimalEdgeDiscovery + +Sandbox API Repository to describe, develop, document, and test the OptimalEdgeDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYAtC) + +## Scope + +* Service API(s) “OptimalEdgeDiscovery” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Discover the optimal regions and zones for their edge cloud application +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/OptimalEdgeDiscovery/releases/tag/r1.2) (Fall25), with the following API versions: + * **optimal-edge-discovery v0.1.0** + [[YAML]](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/r1.2/code/API_definitions/optimal-edge-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/OptimalEdgeDiscovery/r1.2/code/API_definitions/optimal-edge-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/OptimalEdgeDiscovery/r1.2/code/API_definitions/optimal-edge-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/OptimalEdgeDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/OptimalEdgeDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/OptimalEdgeDiscovery/code/API_definitions/README/raw.md b/marked/OptimalEdgeDiscovery/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/OptimalEdgeDiscovery/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery/raw.md b/marked/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..46e3ba3fa66c43fcaa37e573dde649b054f70f70 --- /dev/null +++ b/marked/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery/raw.md @@ -0,0 +1,844 @@ +# optimal-edge-discovery + +```yaml +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Optimal Edge Discovery + version: wip + x-camara-commonalities: 0.6 + description: | + # Introduction + --- + The Optimal Edge Discovery API is designed to help users discover the + optimal edge cloud zones for their applications. This API allows users to + find the optimal regions and zones to deploy their edge cloud applications + based on the device's location, network characteristics and the application + profile. + + ## Features + - Discover regions and zones to deploy edge cloud applications. + + ## Usage + Users can utilize this API to enhance the performance and connectivity of + their applications by selecting the most suitable edge cloud zones and + application endpoints. + + These APIs may be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet) or by the application + server for following scenarios: + + - **Edge Cloud Region Discovery**: To discover the regions where edge + cloud zones are available. Developers can use this information to + understand the geographical coverage of edge cloud services before + deciding where to deploy their applications or before using the more + specific optimal edge discovery functionality. + This can be achieved using the `/regions` API. + + - **Edge Cloud Zone Discovery**: To find the optimal edge cloud + zones to deploy application to minimize latency for users in a specific + region. This can be achieved using the + `/retrieve-optimal-edge-cloud-zones` API. + + To call these endpoints, the API consumer must first obtain a valid OAuth2 token + from the token endpoint, and pass it as an `Authorization` header in the API + request. + + # Identifying the device + + The API returns the closest Edge Cloud Zone to a given device, so that + device needs to be identifiable by the network. This can be achieved either + by passing one or more device identifiers in the request, or, from the + three-legged access token where implemented by the operator. + + ## Passing device identifier(s) in the request + At least one of the following device identifiers must be provided, unless + using a 3-legged access toekn (see next section): + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + + NOTE1: the network operator might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the + same device. + + NOTE2: for this Commonalities release, we are enforcing that the + `networkAccessIdentifier` is only part of the schema for future-proofing, and + CAMARA does not currently allow its use. After the CAMARA meta-release work + is concluded and the relevant issues are resolved, its use will need to be + explicitly documented in the guidelines. + + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will be + identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier + MUST NOT be provided, as the subject will be uniquely identified from the access + token. + + This approach simplifies API usage for API consumers using a three-legged access + token to invoke the API by relying on the information that is associated with the + access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` + object is not included in the request, then the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` + object is also included in the request, then the server will return an error with the + `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device + is identified by these two methods, as the server is unable to make this comparison. + + # Responses + + ## Success + + A JSON object is returned containing an array with a single member object. + This contains identifiers for the closest Edge Cloud Zone. The HTTP status + code will be`200 OK`. An example response: + + ``` + { + "edgeCloudZones": [ + { + "edgeCloudZoneId": "7ab123-9087-6543-ef12-3dc45f67gh89", + "edgeCloudZoneName": "Example Zone Name", + "edgeCloudProvider": "Example Zone Provider", + "edgeCloudRegion": "us-west-1", + "edgeCloudZoneStatus": "active" + } + ], + "applicationProfileId": "2fa85f64-5717-4562-b3fc-2c963f66afa0", + "device": { + "phoneNumber": "+123456789" + } + } + ``` + * `edgeCloudZoneId` is a UUID for the Edge Cloud Zone. + * `edgeCloudZoneName` is the common name of the closest Edge Cloud Zone to + the user device. + * `edgeCloudProvider` is the name of the operator or cloud provider of + the Edge Cloud Zone. + * `edgeCloudRegion` is the region of the closest Edge Cloud Zone to + the user device. + * `edgeCloudZoneStatus` is the status of the Edge Cloud Zone (default is 'unknown'). + * `edgeCloudZones` is an array of Edge Cloud Zones that match the query + parameters. The array will contain at least one Edge Cloud Zone, and + may contain multiple Edge Cloud Zones if there are multiple zones that + match the query parameters. + * `applicationProfileId` is the reference ID associated with the + application profile. This is a UUID that identifies the application + profile for which the Edge Cloud Zones are being discovered. + * `device` is an object containing the device identifier used to + determine the user's location. This object will contain one of the + following identifiers: + - `phoneNumber`: The phone number of the device in E.164 format. + - `networkAccessIdentifier`: The network access identifier assigned by + the mobile network operator for the device. + - `ipv4Address`: The public IPv4 address and port of the device. + - `ipv6Address`: The public IPv6 address of the device. + The response will contain only one of these identifiers, depending on + which identifier was used to identify the device in the request. + If the device was identified from the access token, the `device` object + will not be present in the response, and the `applicationProfileId` will + be the only field returned. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Notes for Optimal Edge Discovery API publishers + + Should your implementation require the `Port` value to be passed in addition + to the `IP-Address`, please make that explicit in the documentation, and + utilise the `GENERIC_400_MISSING_PORT` error if the `Port` header is + omitted. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + --- + + license: + name: Apache 2.0 + url: "https://www.apache.org/licenses/LICENSE-2.0.html" +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/OptimalEdgeDiscovery + +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/optimal-edge-discovery/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` +############################################################################ +# Tags # +############################################################################ +tags: + - name: Regions + description: | + Get all Region IDs and Names for edge cloud zones + - name: Discovery + description: | + Discover the regions and zones in the edge cloud + application, find optimal edge cloud zones for + your deployed applications, and optimal + Application Endpoints for your clients to connect to. +############################################################################ +# Paths # +############################################################################ +paths: + /regions: + get: + summary: Fetch all Regions + operationId: getRegions + security: + - openId: + - "optimal-edge-discovery:regions:read" + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Returns Edge Cloud Regions + content: + application/json: + schema: + title: GetEdgeCloudRegionsResponse + type: array + items: + $ref: "#/components/schemas/EdgeCloudRegion" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Regions + description: | + This is a helper API to get all the regions. The response identifies the + regions where edge cloud zones are available. + /retrieve-optimal-edge-cloud-zones: + post: + operationId: discoverOptimalEdge + security: + - openId: + - "optimal-edge-discovery:edge-zones:read" + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: false + content: + application/json: + schema: + $ref: "#/components/schemas/OptimalEdgeDiscoveryInfo" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + description: returns optimal edge cloud zone matching query + parameters + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/EdgeDiscoveryResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Discovery + summary: Discover optimal edge cloud zones for deployed applications + description: Returns a list of optimal edge cloud zones where you can + register your deployed application. You can choose to search without + passing any of the inputs parameters or a combination of Application + Profile and device information. + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + EdgeDiscoveryResponse: + type: object + description: | + Response for the optimal edge discovery API. It contains a list of + edge cloud zones that match the query parameters. + properties: + edgeCloudZones: + type: array + items: + $ref: "#/components/schemas/EdgeCloudZone" + minItems: 1 + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/DeviceResponse" + + EdgeCloudZone: + type: object + description: Edge cloud zone information for the + given application profile and device information + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + + ApplicationProfileId: + type: string + format: uuid + description: reference id associated to application profile + + EdgeCloudZoneId: + description: | + Operator-issued UUID for the Edge Cloud Zone. + type: string + format: uuid + additionalProperties: false + + EdgeCloudZoneName: + description: | + The name of the operator or cloud provider of the Edge Cloud Zone. + type: string + additionalProperties: false + + EdgeCloudProvider: + description: | + The company name of the Edge Cloud Zone provider. + type: string + + EdgeCloudRegion: + description: | + The common name of the closest Edge Cloud Zone to the user device. + type: string + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + OptimalEdgeDiscoveryInfo: + description: | + Resource to obtain the optimal edge cloud zone for a given application + profile and device information. The API returns the closest Edge Cloud + Zone to a given device, so the device needs to be identifiable by the + network. This can be achieved either by passing a device identifier in + the request header, or, from the 3-legged access token where implemented + by the operator. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + required: + - applicationProfileId + + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their + request, the API provider must return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do not + match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers + with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. + Examples of devices include smartphones or IoT sensors/actuators.The + developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. + In mobile networks it corresponds to the MSISDN + (Mobile Station International Subscriber Directory Number). In order to + be globally unique it has to be formatted in international format, + according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a + mobile network. In 3GPP terminology, it corresponds to the GPSI + formatted with the External Identifier + ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, + the network access identifier is not subjected to portability ruling in + force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) + IP address and port as seen by the application server, or the + private (local) and any public (observed) IP addresses in use by the + device (this information can be obtained by various means, for example + from some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. If NAT64 is in use, the device should + be identified by its publicAddress and publicPort, or separately by its + allocated IPv6 address (field ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ###################################################### + # RESPONSES + ####################################################### + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, + request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter criteria + combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or + expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the + device or phone number identification cannot be derived from the + 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is + supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or + phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due + to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" +``` diff --git a/marked/OptimalEdgeDiscovery/documentation/API_documentation/README/raw.md b/marked/OptimalEdgeDiscovery/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/OptimalEdgeDiscovery/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist/raw.md b/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..518d1249acaae6d20aebfd523472894b90604ef3 --- /dev/null +++ b/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# Optimal Edge Discovery API Readiness minimum criteria checklist + +Checklist for Optimal-Edge-Discovery v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/optimal-edge-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/optimal-edge-discovery-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/optimal-edge-discovery.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/N4AtC) | diff --git a/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story/raw.md b/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..47e4a234133bbce051191c78e1e50580f67dfa64 --- /dev/null +++ b/marked/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story/raw.md @@ -0,0 +1,10 @@ +# Optimal Edge Discovery API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to discover the optimal Edge Cloud Zones for deploying my application instances, ensuring my users get the best performance by connecting to edge resources with minimal latency. The Optimal Edge Discovery API allows me to find the Edge Cloud Zones that are closest to a specific device, providing information about their locations, capabilities, and network characteristics. This helps me make informed decisions about where to deploy my application instances to ensure optimal performance for users across different geographical areas. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
                      **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
                      **Scope:**
                      • Discover optimal Edge Cloud Zones for specific devices
                      • Retrieve information about available Edge Cloud Zones and their capabilities
                      • Make informed decisions about application deployment locations
                      | +| ***Pre-conditions*** |The preconditions are listed below:
                      1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
                      2. The API Consumer:BusinessManager has successfully subscribed to the Optimal Edge Discovery product from the product catalog.
                      3. The API Consumer:Administrator has onboarded the developer:User to the platform.
                      4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                      5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.
                      | +| ***Activities/Steps*** | **Starts when:**
                      1. The API consumer application makes a request to discover the optimal Edge Cloud Zones for a specific device, optionally providing filter parameters to narrow down the results.

                      **Ends when:**
                      1. The API endpoint returns information about available Edge Cloud Zones ordered by their proximity to the device. | +| ***Post-conditions*** | 1. The API consumer has information about optimal Edge Cloud Zones for deploying their application instances.
                      2. The API consumer can use this information to make decisions about application deployment or to register application endpoints in these zones. | +| ***Exceptions*** | Several exceptions might occur
                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                      - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                      - Invalid filter: The filter parameters provided are not valid or cannot be applied.
                      - Not Found: No Edge Cloud Zones are available that match the specified criteria.
                      - Identifier Not Found: The device identified in the request cannot be found in the network. diff --git a/marked/OptimalEdgeDiscovery/documentation/SupportingDocuments/README/raw.md b/marked/OptimalEdgeDiscovery/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/OptimalEdgeDiscovery/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/PopulationDensityData/README/raw.md b/marked/PopulationDensityData/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ab236a36df5d922191df41fa28617e3ae0df14a9 --- /dev/null +++ b/marked/PopulationDensityData/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# PopulationDensityData + +Incubating API Repository to evolve and maintain the definitions and documentation of PopulationDensityData Service API(s) within the Sub Project [Population Density Data](https://lf-camaraproject.atlassian.net/wiki/x/LwAwC) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/3DXe) + +## Scope +* Service APIs for “Population Density Data” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * The service enables developers with the capability to get dynamic population density data in a specific area for a specified date&time, considering anonymized information of the network connected devices in the requested area at the flight time. + * Use Case (1): Providing BVLOS flight the data to meet SORA 2.5 requirements in terms of intrinsic Ground Risk Class (iGRC). + * Use Case (2): Providing data to identify if the ground risk class for a given drone flight is acceptable for the time of the flight, or an alternative time should be considered to lower the risk. + * Service Inputs: Area of the interest. Date & time range. + * Service Outputs: maximum, average and minimum population density value for the given area, and interval corresponding to the valid range of that value. (space and time maps). + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Incubating stage since: June 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/PopulationDensityData/releases/tag/r3.2) (Fall25), with the following API versions: + * **population-density-data v0.3.0** + [[YAML]](https://github.com/camaraproject/PopulationDensityData/blob/r3.2/code/API_definitions/population-density-data.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/PopulationDensityData/r3.2/code/API_definitions/population-density-data.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/PopulationDensityData/r3.2/code/API_definitions/population-density-data.yaml) +* The latest public release is always available here: https://github.com/camaraproject/PopulationDensityData/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/PopulationDensityData/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/PopulationDensityData/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Wednesday, 14:00 Europe/Amsterdam (CET) (13:00 UTC, 12:00 UTC during European DST). + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95956472717?password=e4e7e889-ffb8-4fac-9e9d-d9adcaf2e711) + * For date/time of next meeting see previous [ meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/HwPe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/PopulationDensityData/code/API_definitions/population-density-data/raw.md b/marked/PopulationDensityData/code/API_definitions/population-density-data/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1d2820f179f545b2c3379e4fc8d5cd11dcc4ee9b --- /dev/null +++ b/marked/PopulationDensityData/code/API_definitions/population-density-data/raw.md @@ -0,0 +1,1136 @@ +# population-density-data + +```yaml +openapi: 3.0.3 +info: + title: Population Density Data + description: >- + The Population Density Data API exposes population density estimations + for a specified area for a specified time interval. + + # Introduction + + With the Population Density Data API the customer can retrieve population density estimations + for a specific area at the current or a specified period of time. The estimation considers historical + anonymized information of the network connected devices in the requested + area. * Note that the data provided are estimations of population, based on past or future predicted data, for both past or future time ranges. + + + This functionality can be used for multiple use + cases, some of the possible use cases for this API are: + + + - Supporting BVLOS (Beyond Visual Line of Sight) flights with the + information needed to meet SORA 2.5 (Specific Operation Risk Assessment) + requirements in terms of intrinsic Ground Risk Class (iGRC). + More information in [Specific Operations Risk Assessment](https://www.easa.europa.eu/en/domains/civil-drones-rpas/specific-category-civil-drones/specific-operations-risk-assessment-sora) + + - Providing information to identify if the ground risk class for + a given drone flight path is acceptable for the time of the flight, or an + alternative time should be considered to lower the risk. + + - Sustainable Urban Planning. + + - Environmental monitoring at mass events, such as concerts or festivals. + + + The list above is just a few examples, the API can be used for other use cases as well. + + + # Relevant terms and definitions + + * **Population Density**: refers to the number of people in a given area divided by the total size of the area. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. + This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + When an asynchronous response is requested, the 202 response of the API will include an `operationId` property. This `operationId` property will + also be sent in the callback notification. The purpose of the `operationId` is to correlate an asynchronous response with its corresponding request. + + # API Functionality + + Once a developer specifies (1) the area as a polygon shape, (2) a precision level and (3) time interval + in which they want to obtain the population density, the API returns a data + set consisting of a sequence of time ranges, with each time range containing the + input polygon subdivided into equal-sized grid cells. + + + For each of the equal-sized cells of the grid, an estimated population density is + reported for each time slot within the range, this includes: estimated population density people/km2, and a range for this estimation - [minimum, maximum] + (exact definitions of minimum and maximum are estimation algorithm specific). + + + These values are calculated based on historical data, prediction models, and population estimation models. The requested interval must either be completely in the future or in the past. + + The API has the following time constraints for requests: the minimum startTime must cover at least 3 months before the request time, + and the maximum endTime allowed is 3 months from the time of the request. + + The polygon specifying an area of interest must comply with certain restrictions, + which must be previously validated by the developer: + + - The polygon may not exceed a certain area. + + - The polygon may not contain more than 15 vertexes. + + - The polygon must be associated with a location where the MNO provides + mobile connectivity services. If a polygon is located entirely outside the + supported area, an empty array is returned. + + + The standard behaviour of the API is synchronous, although for large + area requests the API may behave asynchronously. An API invoker can enforce + asynchronous behaviour by providing a callback URL (`sink`) + is in the request, in this case the API sends a callback + to the callback URL provided with the result of the request. If `sink` is + included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` + MUST be set to `ACCESSTOKEN` if provided. + + + For requests with a combination of `area`, `precision`, `startTime` and `endTime` + properties involving an amount of processing that cannot be processed synchronously, + the API returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE`. + + + For requests with a combination of `area`, `precision`, `startTime` and `endTime` + properties too big for both synchronous and asynchronous processing, the API + returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST`. + + If an error happens during the asynchronous processing of the request. The API callback + will have property `status` with value `OPERATION_NOT_COMPLETED` as an error cannot be returned in the callback. + The callback will also include the `statusInfo` property to add extra information about the error. + + **NOTE**: In order to ensure anonymized information, if the data relating to + a grid cell in the required time interval is not sufficient to be exposed due + to [k-anonymity](https://en.wikipedia.org/wiki/K-anonymity), no such data is + returned by the API and the value of the dataType property is `LOW_DENSITY`. + + # Resources and Operations overview + + The API provides one endpoint that accepts POST requests for retrieving population + density information in the specified area. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Population Density Data API ensures the usage of anonymized information and do not treat personal data neither as input nor output. + Therefore, the access to Population Density Data API is defined as Client Credentials - 2-legged. Please refer to Identify and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/PopulationDensityData + +servers: + - url: '{apiRoot}/population-density-data/vwip' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Population Density Data + description: Operations to retrieve population density information. +paths: + /retrieve: + post: + tags: + - Population Density Data + summary: Retrieves population density information in a specified area + description: >- + Retrieves population density estimation together with the estimation range related + for a time slot for a given area (described as a polygon) as a data set + consisting of a sequence of equally-sized objects covering the input + polygon area. + operationId: retrievePopulationDensity + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityRequest' + example: + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.75249 + longitude: 4.861876 + - latitude: 45.751224 + longitude: 4.861125 + - latitude: 45.751442 + longitude: 4.859827 + startTime: '2024-04-23T14:44:18.165Z' + endTime: '2024-04-23T14:44:18.165Z' + precision: 7 + required: true + callbacks: + populationDensityDataCallback: + '{$request.body#/sink}': + post: + tags: + - Population Density Data + summary: 'Population Density Data callback' + description: | + Important: this endpoint is to be implemented by the API consumer. + The Population Density Data server will call this endpoint when the request result is ready. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Population density data result. + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityAsyncResponse' + examples: + PopulationDensitySupportedAreaAsyncResponseExample: + $ref: '#/components/examples/PopulationDensitySupportedAreaAsyncResponseExample' + PopulationDensityAreaNotSupportedAsyncResponseExample: + $ref: '#/components/examples/PopulationDensityAreaNotSupportedAsyncResponseExample' + PopulationDensityPartOfAreaNotSupportedAsyncResponseExample: + $ref: '#/components/examples/PopulationDensityPartOfAreaNotSupportedAsyncResponseExample' + PopulationDensityOperationNotCompletedExample: + $ref: '#/components/examples/PopulationDensityOperationNotCompletedExample' + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + '429': + $ref: '#/components/responses/Generic429' + security: + - {} + - notificationsBearerAuth: [] + responses: + '200': + description: Population density data result. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityResponse' + examples: + PopulationDensitySupportedAreaResponseExample: + $ref: '#/components/examples/PopulationDensitySupportedAreaResponseExample' + PopulationDensityAreaNotSupportedResponseExample: + $ref: '#/components/examples/PopulationDensityAreaNotSupportedResponseExample' + PopulationDensityPartOfAreaNotSupportedResponseExample: + $ref: '#/components/examples/PopulationDensityPartOfAreaNotSupportedResponseExample' + + '202': + description: Population density data requested. This response is returned when the behaviour of the API is asynchronous. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AcceptedAsyncResponse' + '400': + $ref: '#/components/responses/RetrieveLocationBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/RetrieveLocationUnprocessableContent422' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - population-density-data:read +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: '{$request.body#sinkCredential.credentialType}' + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PopulationDensityRequest: + type: object + description: >- + Request object for retrieving population density data in a + specified area. + **NOTE**: The difference between `startTime` and `endTime` cannot be greater than 7 days. + properties: + area: + $ref: '#/components/schemas/Area' + startTime: + type: string + format: date-time + description: >- + Start date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + example: "2023-07-03T12:27:08.312Z" + endTime: + type: string + format: date-time + description: >- + End date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + The maximum endTime allowed is 3 months from the time of the request. + example: "2023-07-03T12:27:08.312Z" + precision: + type: integer + description: >- + Precision required of response cells. Precision defines a geohash level and corresponds to the length of the geohash for each cell. More information at [Geohash system](https://en.wikipedia.org/wiki/Geohash)" + If not included the default precision level 7 is used by default. In case of using a not supported level by the MNO, the API returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION`. + minimum: 1 + maximum: 12 + default: 7 + sink: + type: string + format: uri + description: The address where the API response will be asynchronously delivered, using the HTTP protocol. + pattern: ^https:\/\/.+$ + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + required: + - area + - startTime + - endTime + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + POLYGON - The area is defined as a polygon. + enum: + - POLYGON + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + PopulationDensityResponse: + type: object + description: >- + Population density values is represented in time intervals for different + cells of the requested area. Each element in `timedPopulationDensityData` array corresponds + to a time interval, containing population density data for the grid cells. The intervals are 1 hour long. + properties: + timedPopulationDensityData: + type: array + description: >- + Time ranges along with the population density data for the cells within it. + The request startTime or the request endTime have to be fully covered by the intervals. + For example, if the intervals are 1-hour long and the input date range were [2024-01-03T11:25:00Z + to 2024-01-03T12:45:00Z] it would contain 2 intervals (Interval from 2024-01-03T11:00:00Z + to 2024-01-03T12:00:00Z and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + items: + $ref: '#/components/schemas/TimedPopulationDensityData' + status: + $ref: '#/components/schemas/ResponseStatus' + statusInfo: + type: string + description: Information about the status, mandatory when property `status` is `OPERATION_NOT_COMPLETED` for adding extra information about the error. + example: Some error happened during the processing of the request + required: + - timedPopulationDensityData + - status + AcceptedAsyncResponse: + type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + PopulationDensityAsyncResponse: + allOf: + - $ref: '#/components/schemas/PopulationDensityResponse' + - type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + OperationId: + type: string + description: The unique identifier of the asynchronous operation that is returned when the operation is initiated. + ResponseStatus: + type: string + description: >- + Represents the state of the response for the input polygon defined in the request, the possible values are: + - `SUPPORTED_AREA`: The whole request area is supported. Population density data for the entire requested area is returned. + - `PART_OF_AREA_NOT_SUPPORTED`: Part of the requested area is outside the MNOs coverage area, the cells outside the coverage + area will have property `dataType` with value `NO_DATA`. + - `AREA_NOT_SUPPORTED`: The whole requested area is outside the MNOs coverage area. No data will be returned. + - `OPERATION_NOT_COMPLETED`: An error happened during asynchronous processing of the request. This status will only be returned + in case the asynchronous API behaviour is used. + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - OPERATION_NOT_COMPLETED + TimedPopulationDensityData: + type: object + properties: + startTime: + type: string + format: date-time + description: >- + Interval start time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T10:00:00Z" + endTime: + type: string + format: date-time + description: >- + Interval end time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T11:00:00Z" + cellPopulationDensityData: + $ref: '#/components/schemas/CellPopulationDensityDataArray' + required: + - startTime + - endTime + - cellPopulationDensityData + CellPopulationDensityDataArray: + type: array + description: >- + Population density data for the different cells in a concrete time range. + items: + $ref: '#/components/schemas/CellPopulationDensityData' + minItems: 1 + CellPopulationDensityData: + type: object + description: >- + Population density data of a cell in a concrete time range. In case of + insufficient data, to guarantee an anonymized prediction due to the + k-anonymity within a specific cell and time range, no population density + data is returned and the property `dataType` value is "LOW_DENSITY". In + case of a cell not supported `dataType` value is "NO_DATA" + properties: + geohash: + type: string + description: >- + Coordinates of the cell represented as a string using the [Geohash system](https://en.wikipedia.org/wiki/Geohash). + Encoding a geographic location into a short string. The value length, + and thus, the cell granularity, is determined by the request body property `precision`. + example: ezdmemd + dataType: + type: string + enum: + - NO_DATA + - LOW_DENSITY + - DENSITY_ESTIMATION + required: + - geohash + - dataType + discriminator: + propertyName: dataType + mapping: + NO_DATA: '#/components/schemas/NoData' + LOW_DENSITY: '#/components/schemas/LowDensity' + DENSITY_ESTIMATION: '#/components/schemas/DensityEstimation' + NoData: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + LowDensity: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + DensityEstimation: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + - type: object + properties: + maxPplDensity: + type: integer + description: Maximum people/km2 estimated for the defined area. + minPplDensity: + type: integer + description: Minimum people/km2 estimated for the defined area. + pplDensity: + type: integer + description: people/km2 estimation for the defined area. + required: + - maxPplDensity + - minPplDensity + - pplDensity + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + RetrieveLocationBadRequest400: + description: >- + Problem with the client request. In addition to generic scenarios of + `INVALID_ARGUMENT`, `INVALID_CREDENTIAL`, `INVALID_TOKEN`, another scenarios may exist: + - The area is not a polygon shape or exceeds supported complexity ("code": "POPULATION_DENSITY_DATA.INVALID_AREA", "message": "The area is not a polygon shape or exceeds supported complexity") + - Indicated `startTime` is greater than the maximum allowed ("code": "POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED", "message": "Indicated startTime is greater than the maximum allowed") + - Indicated `startTime` is earlier than the minimum allowed ("code": "POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED", "message": "Indicated startTime is earlier than the minimum allowed") + - Indicated `endTime` is earlier than the `startTime` ("code": "POPULATION_DENSITY_DATA.INVALID_END_TIME", "message": "Indicated endTime is earlier than the startTime") + - Indicated time period is partially in the past and partially in the future ("code": "POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD", "message": "time period is partially in the past and partially in the future") + - Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime) ("code": "POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED", "message": "Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime)") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + - POPULATION_DENSITY_DATA.INVALID_AREA + - POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED + - POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED + - POPULATION_DENSITY_DATA.INVALID_END_TIME + - POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED + - POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Invalid input + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + POPULATION_DENSITY_DATA_400_INVALID_AREA: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_AREA + message: The area is not a polygon shape or has an arbitrary complexity + POPULATION_DENSITY_DATA_400_MAX_STARTTIME_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED + message: >- + Indicated startTime is greater than the maximum allowed + POPULATION_DENSITY_DATA_400_MIN_STARTTIME_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED + message: >- + Indicated startTime is earlier than the minimum allowed + POPULATION_DENSITY_DATA_400_INVALID_END_TIME: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_END_TIME + message: Indicated endDate is earlier than the startTime + POPULATION_DENSITY_DATA_400_MAX_TIME_PERIOD_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED + message: >- + Indicated time period is greater than the maximum allowed + (More than maximum hours between startTime and endTime) + POPULATION_DENSITY_DATA_400_INVALID_TIME_PERIOD: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD + message: >- + Indicated time period is partially in the past and partially in the future + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + RetrieveLocationUnprocessableContent422: + description: >- + Problem with the client request. The following scenarios may exist: + - Indicated combination of area, time interval and precision is too big ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST", "message": "Indicated combination of area, time interval and precision is too big") + - Indicated cell precision (Geohash level) is not supported ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION", "message": "Indicated cell precision (Geohash level) is not supported") + - Indicated combination of area, time interval and precision is too big for a sync response ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE", "message": "Indicated combination of area, time interval and precision is too big for a sync response") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST + - POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION + - POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE + examples: + POPULATION_DENSITY_DATA_422_UNSUPPORTED_REQUEST: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST + message: Indicated combination of area, time interval and precision is too big for both synchronous and asynchronous processing + POPULATION_DENSITY_DATA_422_UNSUPPORTED_PRECISION: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION + message: >- + Indicated cell precision (Geohash length) is not supported + POPULATION_DENSITY_DATA_422_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE + message: >- + Indicated combination of area, time interval and precision is too big for synchronous processing + and asynchronous processing is not enabled + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + PopulationDensitySupportedAreaResponseExample: + value: + status: SUPPORTED_AREA + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: LOW_DENSITY + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + PopulationDensityPartOfAreaNotSupportedResponseExample: + value: + status: PART_OF_AREA_NOT_SUPPORTED + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: NO_DATA + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: NO_DATA + PopulationDensityAreaNotSupportedResponseExample: + value: + status: AREA_NOT_SUPPORTED + timedPopulationDensityData: [] + PopulationDensitySupportedAreaAsyncResponseExample: + value: + status: SUPPORTED_AREA + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: LOW_DENSITY + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityPartOfAreaNotSupportedAsyncResponseExample: + value: + status: PART_OF_AREA_NOT_SUPPORTED + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: NO_DATA + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: NO_DATA + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityAreaNotSupportedAsyncResponseExample: + value: + status: AREA_NOT_SUPPORTED + timedPopulationDensityData: [] + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityOperationNotCompletedExample: + value: + status: OPERATION_NOT_COMPLETED + timedPopulationDensityData: [] + statusInfo: Some error happened during the processing of the request + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 +``` diff --git a/marked/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist/raw.md b/marked/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..30fe9f9352509aabe06c6013e8957c24f83a0008 --- /dev/null +++ b/marked/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for population-density-data 0.3.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/population-density-data.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.2) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.2) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.3.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/population-density-data.yaml) | +| 6 | User stories | O | O | O | M | N | TBC | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/population-density-data.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/population-density-data.feature) | +| 9 | Test result statement | O | O | O | M | N | TBC | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | No | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/74448957/PopulationDensityData+API+description) | diff --git a/marked/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02/raw.md b/marked/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..02f9537d351ea7d78fba1c59a2f8cdd9cb8f0863 --- /dev/null +++ b/marked/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02/raw.md @@ -0,0 +1,99 @@ +# CAMARA Population Density Data API - Follow-up meeting #1 - 2024-02-07 + +*February 07th, 2024* + +## Attendees + +|| +| --- | +|Sachin Kumar (Vodafone)| +|Thomas Neubauer (Dimetor)| +|Violeta Gonzalez Fernandez (Telefonica)| +|Jorge Garcia Hospital (Telefonica)| + + + +Population Density Data API minutes: [https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Approval of previous meeting minutes #1 and meeting agenda + * Confluence adoption +* Open issues and PRs + * Issues: #4 + * PRs: #3 #5 +* Timeline and next steps +* AoB + + +## Open Issues & PRs
                      + + +Item | Who | Description +---- | ---- | ---- +[PR#1](https://github.com/camaraproject/PopulationDensityData/pull/1) | Telefonica | Previous meeting material and minutes +[PR#2](https://github.com/camaraproject/PopulationDensityData/pull/2) | Telefonica | Readme update +[PR#3](https://github.com/camaraproject/PopulationDensityData/pull/3) | Verizon | Including new subgroup maintainer +[Issue#4](https://github.com/camaraproject/PopulationDensityData/issues/4) | Telefonica | Innitial scope agreement +[PR#5](https://github.com/camaraproject/PopulationDensityData/pull/5) | Telefonica | Innitial PopulationDensityData API spec proposal + +## Approval of previous meeting minutes & documentation (#1) + +[KO Meeting Minutes](https://github.com/camaraproject/PopulationDensityData/blob/main/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md) + +### Readme modifications (#2) + +Including the description of the group, link to minutes and schedule of the following meetings (also meeting link) + +### Confluence - to be agreed + +CAMARA is moving the documentation (meeting minutes mainly) to the [wiki.camaraproject.org](https://wiki.camaraproject.org/) Confluence webpage. Proposal to be agreed on moving meeting minutes for following meetings in that format from now on. + +Agreement: To be used from next meeting, minutes and agenda will be placed there. + +### New Maintainer (#3) + +Verizon proposed as new maintainer of the API subgroup. + +### API proposal review (#5) + +Different discussions raised during the API review: +* **Information in water zones**: Operators and therefore API can only provide data of those zones where it is operating. Water zones are not considered and current implementation will provive an error in case the requested zone includes a water zone. Dimetor proposes to only provide "nonData" or null response for those specific cells, but not a complete error, concious of the multiple cases where flights will indeed consider wateer zones due to the expected low population density. + +* Open discussion on **default and limit values** for the API characteristics: + * **Minimum and maximum date** minimum and maximum date allowed as requested time range. Currently, 15 minutes is set as the minimum (soonest time target the request can consider), and 1 year for maximum (longer date with information to extrapolate). TBD + + * **Time interval** in the request: Maximum (and minimum) lenght of the time range requested in the API. TBD + + * **Time granularity** in the response: Lenght of the information pieces in which the time interval is subdivided in the response. Default value is proposed in 1hour, so the response will include density information of each 1hour range that can be included in the requested interval. E.g. If request interval is 15minutes to 1 hour, 1 only result will be provided, if 3 hours and 45 minutes are requested, 4 results will be provided (from 0-1, 1-2, 2-3, 3-3:45). TBD + * **Cell size/granularity** in the response: Currently both cell definition systems allow to implement different size of cells. TBD + +* Cell's format in the response: Currently, API support two different formats of defining the cells in which the requested area is divided for providing the information in the response: + * **Boundary Cells**: The cell is defined by a polygon, composed by the internal area bounded by 4 geo positions. *Same solution as in Location Retrieval API + + * **Geohash Cells**: The Coordinates of the cell are representad as a string using the [Geohash system](https://en.wikipedia.org/wiki/Geohash). The value length, and thus the cell granularity, is determined by the implementation. + + Discussion on which mechanisms to restrict, or how to allow developers to select one of them if multiple are supported.\ + + *(Note that optionality in one side implies obligatory for the other, in this case forcing developers to support both options)* + +## Discussion + +Item | Discussion +---- | ---- +[PR#1](https://github.com/camaraproject/PopulationDensityData/pull/1) | Approval of previous meetinge minutes → Approved +[PR#2](https://github.com/camaraproject/PopulationDensityData/pull/2) | Confirmation of subgroup readme information → Noted +[PR#3](https://github.com/camaraproject/PopulationDensityData/pull/3) | Confirm Verizon as new maintainer → Noted +[Issue#4](https://github.com/camaraproject/PopulationDensityData/issues/4) | Close scope of the innitial API → Approved +[PR#5](https://github.com/camaraproject/PopulationDensityData/pull/5) | Review proposal of innitial API code → [Issue#6](https://github.com/camaraproject/PopulationDensityData/issues/6) [Issue#7](https://github.com/camaraproject/PopulationDensityData/issues/7) [Issue#8](https://github.com/camaraproject/PopulationDensityData/issues/8) Oppened for offline Oppened for offline discussion. +AoB | - + +## Next steps +1. Review and close open points PDD → Follow-up meeting #2 +2. Propose innitial draft of algorithm → Follow-up meeting #2 +3. Draft API spec agreement → Follow-up meeting #3 + + +- Next call will be **February 21th, 2024** + +

                      \ No newline at end of file diff --git a/marked/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24/raw.md b/marked/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6f13d1e1a2ca410dc9eaa235bdefca6415cf6dfb --- /dev/null +++ b/marked/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24/raw.md @@ -0,0 +1,65 @@ +# CAMARA Population Density Data API - KO meeting - 2024-01-24 + +*January 24th, 2024* + +## Attendees + +|| +| --- | +|Sachin Kumar (Vodafone)| +|Thomas Wana (Dimetor)| +|Thomas Neubauer (Dimetor)| +|Violeta Gonzalez Fernandez (Telefonica)| +|Jorge Garcia Hospital (Telefonica)| + + + +Population Density Data API minutes: [https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Presentation of the working group + * Density Population Data reference use cases +* Schedule and bi-weekly planification +* Timeline and next steps +* AoB + + +## Open Issues & PRs
                      + + +Item | Who | Description +---- | ---- | ---- +N/A | N/A | N/A + +## Introduction to the working group + +Supporting material: [KO supporting material](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/SupportingDocuments/KO%20-%20Population%20Density%20Data%20Proposal%20for%20Camara%20Standarizationv3.pptx) + +### Scope + +**API definition:** The Population Density Data API enables developers with the capability to get population density estimations for a specific area at a future date and time, considering historical anonymized information of the network connected devices in the requested area. + +**API inputs (TBC):** Geographical area (2D map) and time range (future) + +**API outputs (TBC):** Max, min and average estimated statistics of population density for the required map, divided in uniform cells depending on the accuracy of the data. In a time series, to include information for the complete requested time range + + +### Density Population Data reference use cases + +For the reference use case, the API fills the need of assessing the ground risk to allow safe drone flights by providing estimations of the number of people under a drone flight path. This assessment will be needed every time a drone flight in the specific category need to conduct an operation and will help the operator to identify operational limitations, to develop the appropriate operational procedures and to identify mitigations and safety objectives. More information in [KO supporting material](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/SupportingDocuments/KO%20-%20Population%20Density%20Data%20Proposal%20for%20Camara%20Standarizationv3.pptx) + +## Discussion + +Item | Discussion +---- | ---- +Group Scope | Telefonica shares the proposal to include not only the specification of the API but also the agreement on the required algorithms of prediction and interpolation that are required in the API to provide a homogeneous response among operators. Aggrement reached. +Meeting Schedule | It's agreed to keep KO time schedule to be replicated in the following repetitions of the subgroup meetings.
                      Be-weekly meeting on Wednesday, 14:00 Europe/Amsterdam (CET) (13:00 UTC, 12:00 UTC during European DST), starting February, 7th. +Timeline and next steps | Schedule to close scope, prepare innitial yaml proposal and close RC version is proposed. +AoB | N/A + + + +- Next call will be **February 7th, 2024** + +

                      diff --git a/marked/PopulationDensityData/documentation/MeetingMinutes/README/raw.md b/marked/PopulationDensityData/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/PopulationDensityData/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal/raw.md b/marked/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4602e628731485ff1df4299b08a0ba1e83ee42d6 --- /dev/null +++ b/marked/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal/raw.md @@ -0,0 +1,30 @@ +# Population Density Data API +## Algorithm initial proposal + +This document serves as a reference model for the population density calculation algorithm. It provides an illustrative high-level overview of the steps proposed to determine population density. Designed for developers, this guide is created to enhance understanding and implementation of the algorithm. While it aims to enhance understanding and implementation, it is the responsibility of the developer to create their own algorithm to calculate population density. + +### Inputs for the algorithm: +* Devices connection records data is received pseudonymized or hashed. +* Requested Space is received in the API customers’ request. +### Process is as follows: +

                        +
                      1. Cleanup: Considering one year of historical information, repeated records will be deleted and IOT (non-personal devices) lines records are filtered due to they do not contribute to the process of estimating future population density.
                        +Output 1 → Cleaned list of Devices connection records

                      2. +
                      3. Attribution: A cell is associated with each user in each time interval. +
                        1. For mobile lines with persistent records, the last cell in which each user has been connected in each interval (considering intervals of 15 minutes) will be associated.
                        2. +
                        3. It is common to have intervals for which a user does not show activity, for them it will be assumed that the user remains in the same cell in which he was last seen active.
                        +Output 2 → Valid Users per cell in each time interval

                      4. +
                      5. Counting and Aggregation: A count of users is performed per cell and interval. On this count, a statistical analysis is performed with the elimination of outliers. Records associated with cells with less than K users in each time interval (k – anonymity) per km2 are discarded (to be evaluated according to local regulations).
                        +Output 3 → Total number of Users connected per cell in each time interval, considering privacy.

                      6. +
                      7. Spatial indexing (no personal data is processed): the space will be mapped into units (grids), to associate the grids that overlap with each cell coverage area.
                        +Output 4 → Regular grid covering the required area, over the cells coverage +areas.

                      8. +
                      9. Distribution and aggregation: Taking into account the coverage area of the cell, users are going to be distributed, homogeneously among the grids (currently 150m x 150m or larger) associated with the cell, and the process is repeated for all cells. As we are assuming that the distribution of users in the coverage area of each cell is uniform, we are introducing an error/noise in the distribution of users by time interval, which will be transferred to population density predictions that contribute to reducing the risk of user reidentification. Each grid on the map can typically be served by several cells of different technologies and frequency bands. To obtain the number of users per grid and time interval, an aggregation is performed.
                        +Output 5 → Number of Users per grid, based on distribution in the cells covering that area.

                      10. +
                      11. Prediction: Based on the historical information of users by grid and interval, the prediction of users by grid and interval is made for each time interval of the future. The algorithm identifies a day of the week and time frame for which the prediction is requested. Then, it will read the records associated for the same weekday and time frame for the previous 4 weeks. +The population density forecast for next Tuesday should be similar to the one observed in the last four Tuesdays. The forecast, then, will be the average of the records of the previous 4 Tuesdays at the same time frame.
                        +Output 6 → Users per grid, considering historical and calendar data

                      12. +
                      13. Extrapolation: Finally, the users of the MNO mobile network are extrapolated +taking into account the market shares by geographical area (municipality) to obtain the total number of people (users or not of the mobile network with any operator).
                        +Output 7 → Total population per grid, considering extrapolation towards MNO market share From step 2 onwards, this is aggregated data that does not contain personal information (this is anonymous data). +
                      diff --git a/marked/PopulationDensityData/documentation/SupportingDocuments/README/raw.md b/marked/PopulationDensityData/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/PopulationDensityData/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/PredictiveConnectivityData/README/raw.md b/marked/PredictiveConnectivityData/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5cbc33652a3fdaa8044a19a6902d267e157ba38a --- /dev/null +++ b/marked/PredictiveConnectivityData/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# PredictiveConnectivityData + +Sandbox API Repository to describe, develop, document, and test the PredictiveConnectivityData Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAnBw) + +## Scope + +* Service API(s) “PredictiveConnectivityData” (see APIBacklog.md) +* The API provides the capability to get the estimation of connectivity delivered by 4G/5G networks along a volume/area for a future date, time, and height. +* Use Cases: + * Network Airspace Connectivity Information for Flight Planning: Provides mobile network coverage forecasts in specific geographic areas to help identify “black volumes” and mitigate the risk of losing drone control due to poor connectivity. + * Autonomous Car Routing: Delivers mobile network coverage forecasts along the planned route of an autonomous car to support decision-making in path planning and connectivity-dependent operations. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: April 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/PredictiveConnectivityData/releases/tag/r1.2) (Fall25), with the following API versions: + * **predictive-connectivity-data v0.1.0** + [[YAML]](https://github.com/camaraproject/PredictiveConnectivityData/blob/r1.2/code/API_definitions/predictive-connectivity-data.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/PredictiveConnectivityData/r1.2/code/API_definitions/predictive-connectivity-data.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/PredictiveConnectivityData/r1.2/code/API_definitions/predictive-connectivity-data.yaml) +* The latest public release is always available here: https://github.com/camaraproject/PredictiveConnectivityData/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/PredictiveConnectivityData/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/PredictiveConnectivityData/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + +* Schedule: Monthly on Tuesdays, 10:00–11:00 UTC + (corresponds to 12:00–13:00 CEST, 06:00–07:00 EDT during Daylight Saving Time) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95479380109?password=0386fbda-1fb5-4e1a-8687-7b81fe8cacfa&invite=true) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/PAAnBw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data/raw.md b/marked/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..96af462ce79711bcc94bdbf418e68592ff02c870 --- /dev/null +++ b/marked/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data/raw.md @@ -0,0 +1,1269 @@ +# predictive-connectivity-data + +```yaml +openapi: 3.0.3 +info: + title: Predictive Connectivity Data + description: >- + # Introduction + + With the Dynamic Predictive Connectivity Data API, the consumer can retrieve an estimation of connectivity delivered by 4/5G networks along a volume/area for a future date, time and height. + + This functionality can be used for multiple use cases, some of the possible use cases for this API are: + + - Network Airspace Connectivity Information for Drones: supporting drone flight planning with detailed analysis of mobile network coverage in the airspace across specific geographic areas. + + - Mobile Network Analysis for Autonomous Cars: enabling route planning through in-depth evaluation of mobile network availability. + + The list above is just a few examples, the API can be used for other use cases as well. + + # Relevant Definitions and concepts + + * **AGL**: Means "Above Ground Level" and describes the vertical height + above the ground. + + * **Service Level**: Describes, in measurable terms, the quality of service + a telecommunication provider furnishes a consumer within a given time period. + + * **Network Type**: Refers to the type of connectivity (4G/5G) for which to retrieve data. + + * **Signal Strength**: Raw signal strength measurements in dBm that can be optionally included in the response when supported by the implementation. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. + This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + When an asynchronous response is requested, the 202 response of the API will include an `operationId` property. This `operationId` property will + also be sent in the callback notification. The purpose of the `operationId` is to correlate an asynchronous response with its corresponding request. + + + # API Functionality + + Once a developer specifies (1) the area as a polygon shape, (2) a precision level, (3) the service + level and (4) time interval in which they want to obtain the connectivity estimation, + the API returns a data set consisting of a sequence of time ranges, with each + time range containing the input polygon subdivided into equal-sized grid cells. + + For each of the equal-sized cells of the grid, an analysis of Connectivity Levels + is reported for each time slot within the range, this includes data classified into: + + - `GC`: Means good connectivity. Service level met even in unfavorable conditions. + - `MC`: Means marginal connectivity. Service level might not be met. + - `NC`: Means no connectivity. Service level not met. + - `ND`: No connectivity data. + + Optionally, if supported by the implementation and requested by the client, raw signal strength values in dBm can also be returned for each layer. + + These values are calculated based on network data and/or prediction models trained on + such data. + + The polygon provided must comply with certain restrictions, which must be + previously validated by the developer: + + - The polygon will not exceed a certain area. + - The polygon cannot have an arbitrary complexity (unlimited number of + sides, complex shapes, etc.). + - The polygon must be associated with a location where the telco provides + mobile connectivity services. Cells outside the area supported by the + implementation will not be returned. Therefore, if a polygon is located + entirely outside the supported area, an empty array will be returned. + + The standard behaviour of the API is synchronous, although for large + area requests the API may behave asynchronously. An API invoker can enforce + asynchronous behaviour by providing a callback URL (sink) in the request, + in this case the API sends a callback to the callback URL provided with the + result of the request. If sink is included, it is RECOMMENDED for the + client to provide as well the sinkCredential property to protect the + notification endpoint. In the current version, sinkCredential.credentialType + MUST be set to ACCESSTOKEN if provided. When an asynchronous response is + requested, the 202 response of the API will include an `operationId` + property. This `operationId` property will also be sent in the callback + notification. The purpose of the `operationId` is to correlate an + asynchronous response with its corresponding request. + + ## Error handling: + + For requests with a combination of area, precision, startTime and endTime + properties involving an amount of processing that cannot be processed + synchronously, the API returns the error response + PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE. + + For requests with a combination of area, precision, startTime and endTime + properties too big for both synchronous and asynchronous processing, the API + returns the error response PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST. + + If an error happens during the asynchronous processing of the request. The + API callback will have property status with value OPERATION_NOT_COMPLETED + as an error cannot be returned in the callback. The callback will also + include the statusInfo property to add extra information about the error. + + NOTE: In case the property "Technology" is not included, the quality of connectivity + will be returned considering both 4G and 5G networks. + + # Resources and Operations overview + + The API provides one endpoint that accepts POST requests for obtaining the + connectivity in a concrete area for a concrete service level and network + type/s. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/PredictiveConnectivityData +servers: + - url: "{apiRoot}/predictive-connectivity-data/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Connectivity Data + description: Operations to retrieve connectivity information. +paths: + /retrieve: + post: + tags: + - Connectivity Data + summary: Obtain connectivity information in the specified area + description: >- + Retrieves the connectivity for a concrete area, specifying the + required service level that has to be met in the whole area in the + requested network type/s. Optionally, raw signal strength values can + be included in the response if supported by the implementation. + operationId: retrieveConnectivity + security: + - openId: + - predictive-connectivity-data:read + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/RetrieveConnectivityRequest' + examples: + RetrieveConnectivityRequestWithHeight: + summary: Request with specified height + value: + serviceLevel: C2 + area: + areaType: POLYGON + boundary: + - latitude: 50.735851 + longitude: 7.10066 + - latitude: 50.74 + longitude: 7.11 + - latitude: 50.73 + longitude: 7.12 + startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + height: 50 + RetrieveConnectivityRequestWithoutHeight: + summary: Request without specified height + value: + serviceLevel: C2 + area: + areaType: POLYGON + boundary: + - latitude: 50.735851 + longitude: 7.10066 + - latitude: 50.74 + longitude: 7.11 + - latitude: 50.73 + longitude: 7.12 + startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + required: true + responses: + '200': + description: Connectivity data result. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/ConnectivityDataResponse' + examples: + ConnectivityDataSupportedAreaResponseExample: + $ref: '#/components/examples/ConnectivityDataSupportedAreaResponseExample' + ConnectivityDataWithSignalStrengthResponseExample: + $ref: '#/components/examples/ConnectivityDataWithSignalStrengthResponseExample' + ConnectivityDataPartOfAreaNotSupportedResponseExample: + $ref: "#/components/examples/ConnectivityDataPartOfAreaNotSupportedResponseExample" + ConnectivityDataAreaNotSupportedResponseExample: + $ref: "#/components/examples/ConnectivityDataAreaNotSupportedResponseExample" + ConnectivityDataSupportedAreaResponseWithHeightExample: + $ref: '#/components/examples/ConnectivityDataSupportedAreaResponseWithHeightExample' + '202': + description: Connectivity data requested. This response is returned when the behaviour of the API is asynchronous. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AcceptedAsyncResponse' + '400': + $ref: '#/components/responses/RetrieveConnectivityBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/RetrieveConnectivityUnprocessableContent422' + '429': + $ref: '#/components/responses/Generic429' + callbacks: + connectivityCallback: + '{$request.body#/sink}': + post: + summary: Callback for asynchronous connectivity data retrieval + description: >- + This callback is invoked to provide the result of an asynchronous + connectivity data retrieval request. + operationId: connectivityCallback + parameters: + - name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: '#/components/schemas/XCorrelator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/ConnectivityDataAsyncResponse' + examples: + ConnectivityDataSupportedAreaAsyncResponseExample: + $ref: "#/components/examples/ConnectivityDataSupportedAreaAsyncResponseExample" + ConnectivityDataOperationNotCompletedExample: + $ref: "#/components/examples/ConnectivityDataOperationNotCompletedExample" + required: true + responses: + '204': + description: Callback successfully received. + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: '{$request.body#sinkCredential.credentialType}' + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RetrieveConnectivityRequest: + type: object + description: Request object for retrieving connectivity data in a specified area. + properties: + serviceLevel: + $ref: '#/components/schemas/ServiceLevel' + area: + $ref: '#/components/schemas/Area' + startTime: + type: string + format: date-time + description: >- + Start date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + endTime: + type: string + format: date-time + description: >- + End date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + networkType: + $ref: '#/components/schemas/NetworkType' + precision: + type: integer + description: >- + Precision required of response cells. Precision defines a geohash level and corresponds to the length of the geohash for each cell. More information at [Geohash system](https://en.wikipedia.org/wiki/Geohash)" + If not included the default precision level 7 is used by default. In case of using a not supported level by the MNO, the API returns the error response `PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION`. + minimum: 1 + maximum: 12 + default: 7 + height: + description: >- + Requested prediction height in metres above ground level. + If a prediction height is specified, the response will include only the connectivity data for the layer containing that height. + If no prediction height is specified, the response will include available prediction for all heights. + type: integer + minimum: 0 + maximum: 250 + includeSignalStrength: + type: boolean + description: >- + Optional parameter to request raw signal strength values in dBm for each layer. + If set to true and supported by the implementation, the response will include + signal strength data alongside connectivity quality information. If not supported + by the implementation, this parameter will be ignored and only connectivity + quality will be returned. + default: false + sink: + type: string + format: uri + description: The address where the API response will be asynchronously delivered, using the HTTP protocol. + pattern: ^https:\/\/.+$ + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable the delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + required: + - serviceLevel + - area + - startTime + - endTime + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + POLYGON - The area is defined as a polygon. + enum: + - POLYGON + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + ServiceLevel: + description: >- + Describes the requested communication service level. Although more + categories may be added in the future, for the time being, the possible + service levels are as follows: + - C2: Command and Control. Consists in connecting an unmanned aerial vehicle with its remote controller. This link allows data transmission in both directions, facilitating real-time operation and feedback. + - STREAM_4K: Streaming in 4K quality. + - BEST_EFFORT: This service level provides a qualitative estimation of coverage based on each operator's own prediction models or public coverage maps. It does not imply any guarantee of network performance or service availability. The values of GC, MC, NC, and ND should be interpreted as approximate indicators of expected connectivity quality, not as results derived from standardised thresholds. + type: string + enum: + - C2 + - STREAM_4K + - BEST_EFFORT + NetworkType: + description: >- + Specifies the type of connectivity for which to retrieve data. Allowed + values are `4G` and `5G`. In case the property is not included, the + quality of connectivity will be returned considering both 4G and 5G + networks. + type: string + enum: + - 4G + - 5G + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + ConnectivityDataResponse: + type: object + description: >- + Response that contains information about the requested area connectivity + for the service level selected. + properties: + layerThickness: + description: Thickness in metres of each layer. + type: number + timedConnectivityData: + type: array + description: >- + Time ranges along with the connectivity data for the cells within it. + The request startTime or the request endTime have to be fully covered by the intervals. + For example, if the intervals are 1-hour long and the input date range were [2024-01-03T11:25:00Z + to 2024-01-03T12:45:00Z] it would contain 2 intervals (Interval from 2024-01-03T11:00:00Z + to 2024-01-03T12:00:00Z and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + items: + $ref: '#/components/schemas/TimedConnectivityData' + status: + $ref: '#/components/schemas/ResponseStatus' + statusInfo: + type: string + description: Information about the status, mandatory when property `status` is `OPERATION_NOT_COMPLETED` for adding extra information about the error. + example: Some error happened during the processing of the request + requestedHeight: + type: integer + description: The height in metres above ground level that was requested in the request. This property is only present if a specific height was requested. + nullable: true + example: 50 + required: + - layerThickness + - timedConnectivityData + - status + AcceptedAsyncResponse: + type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + ConnectivityDataAsyncResponse: + allOf: + - $ref: '#/components/schemas/ConnectivityDataResponse' + - type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + OperationId: + type: string + description: The unique identifier of the asynchronous operation that is returned when the operation is initiated. + example: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ResponseStatus: + type: string + description: >- + Represents the state of the response for the input polygon defined in the request, the possible values are: + - `SUPPORTED_AREA`: The whole request area is supported. Connectivity data for the entire requested area is returned. + - `PART_OF_AREA_NOT_SUPPORTED`: Part of the requested area is outside the MNOs coverage area, the cells outside the coverage + area will have property `layerConnectivities` with all items in the array with value `ND`. + - `AREA_NOT_SUPPORTED`: The whole requested area is outside the MNOs coverage area. No data will be returned. + - `OPERATION_NOT_COMPLETED`: An error happened during asynchronous processing of the request. This status will only be returned + in case the asynchronous API behaviour is used. + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - OPERATION_NOT_COMPLETED + TimedConnectivityData: + type: object + description: >- + Represents a time interval with connectivity data for the cells in the + area. Time interval length is + determined by the implementation. The request startTime or the request + endTime have to be fully covered by the intervals. For example, if the + intervals are 1-hour long and the input date range were + [2024-01-03T11:25:00Z to 2024-01-03T12:45:00Z] it would contain 2 + intervals (Interval from 2024-01-03T11:00:00Z to 2024-01-03T12:00:00Z + and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + properties: + startTime: + type: string + format: date-time + description: >- + Interval start time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + example: "2023-07-03T10:00:00Z" + endTime: + type: string + format: date-time + description: >- + Interval end time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + example: "2023-07-03T11:00:00Z" + cellConnectivityData: + $ref: '#/components/schemas/CellConnectivityDataArray' + required: + - startTime + - endTime + - cellConnectivityData + CellConnectivityDataArray: + type: array + description: >- + Connectivity data for the different cells in a concrete time range. + items: + $ref: '#/components/schemas/CellConnectivityData' + minItems: 1 + CellConnectivityData: + description: >- + Represents a rectangular grid cell within the specified area, including + its connectivity data. + properties: + geohash: + type: string + description: >- + Coordinates of the cell represented as a string using the [Geohash + system](https://en.wikipedia.org/wiki/Geohash), encoding a + geographic location into a short string. The value length, + and thus, the cell granularity, is determined by the request body property `precision`. + example: ezdmemd + layerConnectivities: + $ref: '#/components/schemas/LayerConnectivities' + layerSignalStrengths: + $ref: '#/components/schemas/LayerSignalStrengths' + required: + - geohash + - layerConnectivities + LayerConnectivities: + type: array + minItems: 1 + description: >- + Sequence of connectivity quality values in each of the layers in which + the vertical space over the area determined by the `geohash` is + decomposed. All layers are considered having the same `layerThickness` + meters and are ordered consecutively in the array starting from the + ground (First layer will start at 0 meters AGL). So the layer at + index = N would comprise the heights, referenced to AGL, among N * + `layerThickness` meters and (N+1) * `layerThickness` meters. + If a specific height was requested, this array will contain only one element corresponding to the connectivity for the layer at that height. + + The possible connectivity values are: + - GC: Means good connectivity. Service level met even in unfavorable conditions. + - MC: Means marginal connectivity. Service level might not be met. + - NC: Means no connectivity. Service level not met. + - ND: No connectivity data. + + **NOTE**: These connectivity values are relative to the `serviceLevel` + and `networkType` specified in the request. + items: + $ref: '#/components/schemas/Connectivity' + LayerSignalStrengths: + type: array + minItems: 1 + description: >- + Predicted signal strength values in dBm for each layer. This array is optional + and will only be present if the `includeSignalStrength` parameter was set to true + in the request and is supported by the implementation. The array follows the same + structure as `layerConnectivities`, with each element corresponding to the signal + strength in dBm for the same layer index. All layers are considered having the same + `layerThickness` meters and are ordered consecutively starting from the ground + (First layer starts at 0 meters AGL). A null value indicates no signal strength + data is available for that layer. + If a specific height was requested, this array will contain only one element corresponding to the signal strength for the layer at that height. + items: + type: number + format: float + nullable: true + description: Signal strength value in dBm, or null if no data is available + example: -85.5 + Connectivity: + type: string + enum: + - GC + - MC + - NC + - ND + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + RetrieveConnectivityBadRequest400: + description: >- + Problem with the client request. In addition to regular scenario of + `INVALID_ARGUMENT`, `INVALID_CREDENTIAL`, `INVALID_TOKEN`, another scenarios may exist: + - The area is not a polygon shape or has an arbitrary complexity ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA", "message": "The area is not a polygon shape or has an arbitrary complexity") + - Indicated `startTime` is greater than the maximum allowed ("code": "PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED", "message": "Indicated startTime is greater than the maximum allowed") + - Indicated `startTime` is earlier than the minimum allowed ("code": "PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED", "message": "Indicated startTime is earlier than the minimum allowed") + - Indicated `endTime` is earlier than the `startTime` ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME", "message": "Indicated endTime is earlier than the startTime") + - Indicated time period is partially in the past and partially in the future ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD", "message": "time period is partially in the past and partially in the future") + - Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime) ("code": "PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED", "message": "Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime)") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA + - PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME + - PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Invalid input + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_AREA: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA + message: The area is not a polygon shape or has an arbitrary complexity + PREDICTIVE_CONNECTIVITY_DATA_400_MAX_STARTTIME_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED + message: Indicated startTime is greater than the maximum allowed + PREDICTIVE_CONNECTIVITY_DATA_400_MIN_STARTTIME_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED + message: Indicated startTime is earlier than the minimum allowed + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_END_TIME: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME + message: Indicated endTime is earlier than the startTime + PREDICTIVE_CONNECTIVITY_DATA_400_MAX_TIME_PERIOD_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED + message: >- + Indicated time period is greater than the maximum allowed + (More than maximum hours between startTime and endTime) + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_TIME_PERIOD: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD + message: >- + Indicated time period is partially in the past and partially in the future + RetrieveConnectivityUnprocessableContent422: + description: >- + Problem with the client request. In addition to regular scenario of + `INVALID_ARGUMENT`, another scenarios may exist: + - Indicated request is too big for both synchronous and asynchronous processing ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST", "message": "The indicated request is too big for both synchronous and asynchronous processing") + - Indicated cell precision (Geohash level) is not supported ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION", "message": "Indicated cell precision (Geohash level) is not supported") + - Indicated request is too big for synchronous processing and asynchronous processing is not enabled ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE", "message": "The indicated request is too big for synchronous processing and asynchronous processing is not enabled") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE + examples: + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_REQUEST: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST + message: >- + Indicated combination of area, time interval and precision is too big for both synchronous and + asynchronous processing + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_PRECISION: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION + message: >- + Indicated cell precision (Geohash length) is not supported + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE + message: >- + Indicated combination of area, time interval and precision is too big for synchronous processing + and asynchronous processing is not enabled + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + ConnectivityDataSupportedAreaResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: SUPPORTED_AREA + ConnectivityDataPartOfAreaNotSupportedResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T13:00:00Z" + endTime: "2024-01-03T14:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: PART_OF_AREA_NOT_SUPPORTED + ConnectivityDataAreaNotSupportedResponseExample: + value: + layerThickness: 30 + timedConnectivityData: [] + status: AREA_NOT_SUPPORTED + ConnectivityDataSupportedAreaAsyncResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T12:00:00Z" + endTime: "2024-01-03T13:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: SUPPORTED_AREA + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ConnectivityDataOperationNotCompletedExample: + value: + layerThickness: 30 + timedConnectivityData: [] + status: OPERATION_NOT_COMPLETED + statusInfo: Some error happened during the processing of the request + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ConnectivityDataWithSignalStrengthResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + layerSignalStrengths: + - -85.5 + - -84.0 + - -83.0 + - -82.0 + - -81.0 + - null + - null + - null + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + layerSignalStrengths: + - -85.5 + - -84.0 + - -83.0 + - -82.0 + - -81.0 + - -81.5 + - -81.0 + - -85.0 + status: SUPPORTED_AREA + ConnectivityDataSupportedAreaResponseWithHeightExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - geohash: ezdmemc + layerConnectivities: + - GC + status: SUPPORTED_AREA + requestedHeight: 50 +``` diff --git a/marked/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story/raw.md b/marked/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc37a06e706a6826cbf9350491fce0e8799ec9a8 --- /dev/null +++ b/marked/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story/raw.md @@ -0,0 +1,12 @@ +# PredictiveConnectivityData API User Story + +| **Item** | **Details** | +|---------|-------------| +| **_Summary_** | The API provides the capability to get the estimation of connectivity delivered by 4G/5G networks along a volume/area for a future date, time and height. | +| **_Actors and Scope_** | **Scope:**
                      - Retrieve predicted mobile connectivity (4G/5G) for a defined polygonal area, time interval, and height.
                      - Supports planning in aerial and terrestrial domains.

                      **Use Case 1 – Network Airspace Connectivity Information (forecast) for Flight Planning:**
                      - Delivers comprehensive analysis with data about mobile network coverage in specific geographic areas.
                      - Identifies “black volumes” to avoid drone disconnection risks.

                      **Use Case 2 – Autonomous Car:**
                      - Provides predicted mobile network coverage data along the vehicle route. | +| **_Pre-conditions_** | – The client must provide the following inputs:
                      1. **Requested Area:** polygonal area defined by coordinates forming a closed loop (Required)
                      2. **Start Time** future controlled time of departure (Required). **End Time:** future controlled time of arrival (Required).
                      3. **Service Level:** type of service needed (e.g., C2, STREAM_4K) (Required)
                      4. **Technology:** 4G or 5G (Optional)
                      5. **Height** and **Precision** (as suggested in scope evolution discussions) | +| **_Activities/Steps_** | - The client submits a request including the inputs listed above.
                      - The API responds with:
                      1. An array of cells (Geohash-encoded) with hourly connectivity predictions:
                          - GC: Good Connectivity
                          - MC: Marginal Connectivity
                          - NC: No Connectivity
                      2. Layer thickness in meters (AGL)
                      – Output may optionally include **Signal Strength** instead of **Service Level**. | +| **_Post-conditions_** | The requester obtains connectivity forecasts that support planning for flight or vehicle route safety based on mobile network availability. | +| **_Exceptions_** | Several exceptions might occur during the PredictiveConnectivityData API operations:
                      - **Invalid input:** Required fields missing or incorrectly formatted (e.g., malformed polygon, missing Start/End Time or Service Level).
                      - **Unsupported values:** Inputs that exceed defined limits (e.g., time window too far in the future, unsupported technology type).
                      - **Unavailable data:** The requested area, time, or combination of parameters does not match any available prediction dataset. | + + diff --git a/marked/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist/raw.md b/marked/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..72380213c3393175aa4e578b8c11afd9ff7134d3 --- /dev/null +++ b/marked/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist/raw.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for predictive-connectivity-data v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/predictive-connectivity-data.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3)*** | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0 | +| 5 | API documentation | M | M | M | M | Y | [inline in YAML](/code/API_definitions/predictive-connectivity-data.yaml) | +| 6 | User stories | O | O | O | M | N | [link](/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.mdd) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/predictive-connectivity-data.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/predictive-connectivity-data.feature) | +| 9 | Test result statement | O | O | O | M | N | TBC | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | No | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/owAjBw) | + +*** *The asynchronous response currently does not follow the CloudEvents delivery format as required by Commonalities r3.3. See Issue [#38](https://github.com/camaraproject/PredictiveConnectivityData/issues/38). This will be addressed post-Fall’25 and released as v0.2.0 to ensure full compliance* + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/QoSBooking/README/raw.md b/marked/QoSBooking/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..084502696a536c03acf363c432a1f290da7f84fb --- /dev/null +++ b/marked/QoSBooking/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# QoSBooking + +Sandbox API Repository to describe, develop, document, and test the QoSBooking Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/SADHB) + +## Scope + +* Service API(s) “QoSBooking” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * book an assignment of a certain QoS Profile to a certain device with some conditions such as start time, duration and location in advance. + * update the booking, remove it, and get the information of it. +* Describe, develop, document, and test the API(s) +* Started: January 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/QoSBooking/releases/tag/r1.2) (Fall25), with the following API versions: + * **qos-booking-and-assignment v0.1.0** + [[YAML]](https://github.com/camaraproject/QoSBooking/blob/r1.2/code/API_definitions/qos-booking-and-assignment.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking-and-assignment.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking-and-assignment.yaml) + * **qos-booking v0.1.0** + [[YAML]](https://github.com/camaraproject/QoSBooking/blob/r1.2/code/API_definitions/qos-booking.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking.yaml) +* The latest public release is always available here: https://github.com/camaraproject/QoSBooking/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/QoSBooking/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/QoSBooking/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly on Friday at 13:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94112812156?password=f238d6af-c959-48d7-a862-abdb3c648e40) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/ABje) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/QoSBooking/code/API_definitions/qos-booking-and-assignment/raw.md b/marked/QoSBooking/code/API_definitions/qos-booking-and-assignment/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0c176333e40c1c0a90c71ed3ec4791afd6929094 --- /dev/null +++ b/marked/QoSBooking/code/API_definitions/qos-booking-and-assignment/raw.md @@ -0,0 +1,2103 @@ +# qos-booking-and-assignment + +```yaml +openapi: 3.0.3 +info: + title: QoS Booking and Assignment + description: | + This API enables API consumers to request, in advance, certain network performance to be provided by Telco networks, without having in-depth knowledge of the underlying network complexities (e.g. the 4G/5G system in case of a mobile network) for a number of devices, at a given location, for a period of time. + + The API enables API consumers to book a specific QoS profile for one or more devices with conditions such as the start time, duration and location. Once the booking is confirmed the enduser can assign devices to the booking. + The network operator will provision and activate those devices with the required and agreed network quality at the given time and conditions + + # Relevant terms and definitions + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the network operator for the device, at the request time. After the booking request is accepted, the device may get different IP addresses, but the booking will still apply to the device that was identified during the request process. Note: Network Access Identifier is defined for future use and will not be supported with v0.1 of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (e.g. duration expiration) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # Resources and Operations overview + The API defines seven major operations in two groups: + + Booking: + + - An operation to setup a new QoS Booking for one or more devices. + - An operation to get the information about an existing QoS Booking, identified by its `BookingId`. + - An operation to terminate an existing QoS Booking, identified by its `BookingId`. + + Device Assignment: + + - An operation to assign one or more devices to the existing booking identified by its `BookingId`. + - An operation to release one or more devices from the booking identified by its `BookingId`. + - An operation to get all the devices assigned to a given booking identified by its `BookingId`. + - An operation to get all the associated QoS Booking for a given device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` or `devices` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. In this case, only one device can be provided at a time. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS booking in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QoSBooking + +servers: + - url: "{apiRoot}/qos-booking-and-assignment/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: QoS Booking + description: Book and manage QoS for multiple devices in advance + - name: Device Assignment + description: Manage the assignment of devices for a given QoS Booking + +paths: + /qos-bookings: + post: + tags: + - QoS Booking + summary: This operation reserves required QoS in advance up to a certain number of devices in certain serviceArea and time slot. The devices have to be attached with a subsequent operation. + description: | + This operation reserves a Quality of Service (QoS) booking for a specified number of devices, service area, and scheduled time/duration. + Devices can be assigned to the booking at any time after the reservation is successful and before the scheduled end-time. + - `Pre-assigned devices :` These devices will be automatically provisioned and activated with the requested QoS profile exactly when the scheduled start time arrives. + - `Late-assigned devices:` Devices assigned after the schedule starts (but before it ends) will be provisioned and activated with the requested QoS profile immediately upon assignment. + This operation will return with the following responses: + - `HTTP 201 (status: SUCCESSFUL):` The operator was able to confirm the booking immediately. + - `HTTP 202 (status: PENDING). :` The operator is unable to confirm immediately, and the booking status is pending. A subsequent notification will be sent to confirm the final status, if available. + - `HTTP 4xx (Failure Condition) :` The operator determined that the booking is unavailable. The response will include specific status codes and descriptions detailing the error. + - Respective `statusInfo` contains additional information under certain conditions. + operationId: createBooking + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Input Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInput" + examples: + BOOKING_INPUT_1: + $ref: "#/components/examples/BOOKING_INPUT_1" + BOOKING_INPUT_2: + $ref: "#/components/examples/BOOKING_INPUT_2" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Booking notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Booking change related event occurs. + operationId: postBookingNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Booking creation is successful. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_SUCCESSFUL: + $ref: "#/components/examples/BOOKING_SUCCESSFUL" + "202": + description: | + Booking request is accepted but pending. + Confirmation of success or failure will be sent as a callback notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_PENDING: + $ref: "#/components/examples/BOOKING_PENDING" + "400": + $ref: "#/components/responses/CreateBookingOrAssign400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:create" + + /qos-bookings/{bookingId}: + get: + tags: + - QoS Booking + summary: Get the Booking information for a given QoS Booking identified by `bookingId`. + description: | + This operation is synchronous and retrieves the details of an existing Quality of Service (QoS) booking using its unique identifier (`bookingId`). This `bookingId` is the identifier returned by the initial booking operation upon successful creation. + Response Scenarios: + - `HTTP 200 (status: SUCCESSFUL):` The booking details are successfully retrieved and returned in the response body along with the remaining number of devices still can be assigned to the booking. + - `HTTP 4xx (Failure Condition) :` The request failed, and an appropriate HTTP 4xx error code is returned with a specific status and description. + operationId: getBookingById + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_RETRIEVED: + $ref: "#/components/examples/BOOKING_RETRIEVED" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:read" + + delete: + tags: + - QoS Booking + summary: This operation cancels an existing QoS Booking and release the associated resources. + description: | + This operation cancels and deletes a specific QoS booking using its unique identifier and releases the resources related to that booking. It supports both synchronous and asynchronous processing. + Constraints & Notes: + - The Quality of Service (QoS) booking must have been created by the same API client identified in the access token. + - The SUCCESSFUL and FAILURE conditions for a deletion are dependent on the operator's specific implementation. + - Operators SHOULD properly document their `Booking Cancellation` behavior with clear policies and the respective terms and conditions. + Response Scenarios: + - `HTTP 200 (status: SUCCESSFUL):` The booking was deleted immediately (synchronous success). + - `HTTP 202 (status: PENDING). :` The request has been accepted for processing, but the deletion is not yet complete (asynchronous processing). A subsequent notification will be sent to confirm the final status. + - `HTTP 4xx (Failure Condition) :` The request failed, and an appropriate HTTP 4xx error code is returned with a specific status and description. + operationId: deleteBooking + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Booking deleted. `status` in the response will be `SUCCESSFUL` and `statusInfo` will be `BOOKING_CANCELLED` + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_CANCELLED: + $ref: "#/components/examples/BOOKING_CANCELLED" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `PENDING` and `statusInfo` will be `DELETE_REQUESTED` + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + CANCELLATION_PENDING: + $ref: "#/components/examples/CANCELLATION_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:delete" + + /qos-bookings/{bookingId}/devices/assign: + post: + tags: + - Device Assignment + summary: Assign one or more devices to an existing QoS Booking identified by `bookingId` + description: | + This endpoint allows the end user to assign one or more devices to the existing QoS Booking. + - If the assignment is successful for all the devices, the call will return 201 success code with status `SUCCESSFUL` and the network is available for the said devices to connect and use them at the requested time + - If the assignment request failed for some reason, this call we be retured with 4xx error code with appropirate status codes + - This is an asynchronous call, and status = `PENDING` if the network is still working on your request. A callback will come with appropriate status. + - If the network could not assign all the requested devices, then status = `PARTIAL_SUCCESS` and the `statusInfo` will have additional information. + - If a 2-legged access token is used, then the device details SHOULD BE provided as part of the input, and the output will return the array of actually assigned devices. + - If a 3-legged access token is used, then the device information are identified from the access token, so only one device is implicitly assigned, and the return value may not contain the assigned device information + operationId: assignDevices + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInput" + examples: + ASSIGNMENT_INPUT_1: + $ref: "#/components/examples/ASSIGNMENT_INPUT_1" + ASSIGNMENT_INPUT_2: + $ref: "#/components/examples/ASSIGNMENT_INPUT_2" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Assignment notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Assignment change related event occurs. + operationId: postAssignmentNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: At least one device is assigned to the booking. The developer can call this endpoint multiple times with appropriate information + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_SUCCESSFUL: + $ref: "#/components/examples/ASSIGNMENT_SUCCESSFUL" + ASSIGNMENT_PARTIAL_SUCCESS: + $ref: "#/components/examples/ASSIGNMENT_PARTIAL_SUCCESS" + ASSIGNMENT_FAILURE_1: + $ref: "#/components/examples/ASSIGNMENT_FAILURE_1" + ASSIGNMENT_FAILURE_2: + $ref: "#/components/examples/ASSIGNMENT_FAILURE_2" + + "202": + description: | + Assignment request is accepted but pending decision. + Once the decision is made a callback notification will be sent with appropirate success or failure Confirmation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_PENDING: + $ref: "#/components/examples/ASSIGNMENT_PENDING" + + "400": + $ref: "#/components/responses/CreateBookingOrAssign400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:create" + + /qos-bookings/{bookingId}/devices: + get: + tags: + - Device Assignment + summary: Get the list of devices assigned to an existing QoS Booking + description: | + This endpoint allows the end user to retrieve the list of devices assigned to the existing QoS Booking. + - status = `SUCCESSFUL` if the operation is successful + - status = `FAILURE` if the operation is unsuccessful then the `statusInfo` will have more information. + - GET may not return the identifying details of all the devices assigned to the booking. There are certain situations, identifying details of certain devices can't be disclosed because of privacy laws, jurisdiction restrictions, and some legal requirements. + In such a situation the operator SHOULD properly communicate this to the API consumer that device identifiers of certain devices are not disclosed. `statusInfo` = `DEVICE_DISCLOSURE_POLICY_APPLIED` + - The API consumer can determine; how many devices are actually in the booking from 'bookingDetails'; but may not know the identifying details of all those devices. + - A classic example is: Some of the devices are assigned using a 3-legged access token; Or a booking is made in one jurisdiction and the actual usage is happening in another jurisdiction which has several privacy restrictions. + + operationId: getDevicesByBookingId + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: List of all devices assigned to the booking is returned. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RETRIEVED_1: + $ref: "#/components/examples/ASSIGNMENT_RETRIEVED_1" + ASSIGNMENT_RETRIEVED_2: + $ref: "#/components/examples/ASSIGNMENT_RETRIEVED_2" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:read" + + /qos-bookings/{bookingId}/devices/release: + post: + tags: + - Device Assignment + summary: Release one or more devices from the given QoS Booking + description: | + This endpoint will release one or more assigned devices. The timing of the release depends on the current status: + + - `Before the scheduled time:` The release will be mostly immediate. + - `After the scheduled time (devices active):` The release may take time as the system needs to free up associated resources. + + A callback notification will be sent once the devices are successfully released, provided one is registered with the device assignment. This endpoint functions in both synchronous and asynchronous modes. + - If the device is assigned using 3-legged access token: + - If the device is active, then release can happen in the same way. + - If the device has failed for some reason, and the device information is not known, then the device can't be released from booking. + - This call uses the POST method to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via DELETE. + operationId: releaseDevices + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to release devices + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInput" + examples: + ASSIGNMENT_RELEASE_INPUT: + $ref: "#/components/examples/ASSIGNMENT_RELEASE_INPUT" + required: true + responses: + "200": + description: | + At least one of the requested devices has been successfully released from the booking. + + Example: + + If an end-user requests to release two devices but the network can release only one: + - The `status` will be `PARTIAL_SUCCESS`. + - The `statusInfo` field will contain additional details. + + The returned message body will also contain the list of the actual devices that were released. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RELEASED: + $ref: "#/components/examples/ASSIGNMENT_RELEASED" + "202": + description: | + The release request is accepted but is pending for internal reasons, or the release process has started and is currently in progress. + Once all devices are released, a callback notification will be sent with the appropriate success or failure confirmation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RELEASE_PENDING: + $ref: "#/components/examples/ASSIGNMENT_RELEASE_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:delete" + + /qos-bookings/retrieve: + post: + tags: + - Device Assignment + summary: Retrieves all the bookings that corresponds to a device + description: | + Querying for QoS Booking resource information details for a device. + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The QoS Booking must have been created by the same API client given in the access token. + - If no QoS booking is found for the requested device, an empty array is returned. + - This call uses the POST method to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + operationId: retrieveBookingByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve a booking by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingByDevice" + examples: + RETRIEVE_BOOKINGS_INPUT: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_INPUT" + required: true + responses: + "200": + description: Returns the QoS booking information for a given device. A device may have multiple bookings (for several times and locations), thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingsOutput" + examples: + RETRIEVE_BOOKINGS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_ONE_ITEM" + RETRIEVE_BOOKINGS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_NO_ITEMS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:retrieve-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + BookingId: + name: bookingId + in: path + description: Booking ID that was obtained from the createBooking operation + required: true + schema: + $ref: "#/components/schemas/BookingId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + BookingId: + description: Booking Identifier in UUID format + type: string + format: uuid + + BookingInput: + description: | + Basic input that are required to book QoS in advance. `numDevices` represents the maximum number of devices the enduser wants the operator to reserve in advance. + allOf: + - type: object + properties: + numDevices: + $ref: "#/components/schemas/DeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + sink: + type: string + format: uri + pattern: "^https:\/\/.+$" + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + - startTime + - duration + - serviceArea + + BookingDetails: + description: | + The details of booking. This schema can be used in any place booking details need to be returned. + + allOf: + - type: object + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + totalDevices: + $ref: "#/components/schemas/DeviceCount" + remainingDevices: + $ref: "#/components/schemas/RemainingDeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + required: + - bookingId + - remainingDevices + - qosProfile + - startTime + - duration + - serviceArea + + BookingOutput: + description: | + - If the booking endpoint returns synchronously, `BookingOutput` will be part of the return message body. For async success a follow-up `get` endpoint will return the details of the actual booking. + - It returns original number of devices that are requested as well as the remaining number of devices in the booking that can be assigned + `remainingDevices` >= 0 and <= `totalDevices` + - Once a device is successfully assigned to the booking, `remainingDevices` will be reduced by 1, and once the device is released then it will be incremented by 1 + - Booking Information is also returned as part of the message body when the devices are successfully assigned to the booking. + - `bookingId` may not be present if the booking was not successful + + allOf: + - type: object + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + totalDevices: + $ref: "#/components/schemas/DeviceCount" + remainingDevices: + $ref: "#/components/schemas/RemainingDeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/BookingStatusInfo" + required: + - remainingDevices + - qosProfile + - startTime + - duration + - serviceArea + - status + + DeviceAssignmentInput: + description: | + Array of devices that needs to be assigned to a booking. + - The size of the array should be less than or equal to the devices that are remaining in the original booking. + - At least one device identifier is required when a 2-legged access token is used. + - In a 3-legged situation, only one device can be assigned at a time, and the device details are automatically generated from the access token + - In such a situation, `Devices` array SHOULD NOT be provided. + type: object + properties: + devices: + $ref: "#/components/schemas/Devices" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + + DeviceAssignmentOutput: + description: | + This schema is used to return device information associated with the booking as an output. + - It will have the `bookingDetails` along with all the originally requested information. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + - For example: + - If there are 10 devices assigned in a booking; but the GET operation returns only 7; It means 3 devices can't be disclosed + - The source of truth is in the following properties in the booking details: `totalDevices` and `remainingDevices`. + - In such a situation the operator SHOULD set `statusInfo` as `DEVICE_DISCLOSURE_POLICY_APPLIED` to clearly communicate the fact that some devices are not disclosed. + + allOf: + - type: object + properties: + bookingDetails: + $ref: "#/components/schemas/BookingDetails" + devices: + $ref: "#/components/schemas/DeviceResponseArray" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - status + + RetrieveBookingByDevice: + description: Attributes to look for QoS Booking + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveBookingsOutput: + description: QoS bookings for a given device + type: array + items: + $ref: "#/components/schemas/BookingDetails" + minItems: 0 + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the [QoS Profile API](link TBC). + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-booking-and-assignment.v0.status-changed" + - "org.camaraproject.qos-booking-and-assignment.v0.assignment-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-booking-and-assignment.v0.status-changed: "#/components/schemas/EventBookingStatusChanged" + org.camaraproject.qos-booking-and-assignment.v0.assignment-status-changed: "#/components/schemas/EventAssignmentStatusChanged" + + + EventBookingStatusChanged: + description: Event to notify a QoS Booking status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - bookingDetails + - status + properties: + bookingDetails: + $ref: "#/components/schemas/BookingOutput" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/BookingStatusInfo" + required: + - data + + EventAssignmentStatusChanged: + description: Event to notify a Device Assignment status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - status + - deviceDetails + properties: + deviceDetails: + $ref: "#/components/schemas/DeviceAssignmentOutput" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - data + + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Time: + description: | + Date and time when the API consumer requests the QoS profile to become available. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:31Z" + + Duration: + description: | + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). + Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + The actual value may be limited by QoS Profile. + type: integer + format: int32 + minimum: 1 + example: 3600 + + Devices: + description: | + Array of devices to be assigned to the booking and provisioned. At least one device is required. + Not to be provided when a 3-legged access token already identifies a device. + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Device" + + DeviceResponseArray: + description: List of device identifiers that have been successfully assigned based on the request. + type: array + minItems: 1 + items: + $ref: "#/components/schemas/DeviceResponse" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Status: + description: | + The current status of the requests in any of the endpoints in Booking or Assignment. The status can be one of the following: + * `PENDING` - The request is still being processed. For booking, booking is requested and for assignments, the request is pending. 'statusInfo' may have additional information. + * `SUCCESSFUL` - The request is processed successfully. This may happen immediately. The state will go to PENDING and then back to SUCCESSFUL in certain conditions. + * `PARTIAL_SUCCESS` - The request is processed with partial success - applicable to device assignments. `statusInfo` may have additional information. This enum is optional, and useful if the operator wants to communicate partial success. + * `FAILURE` - The request has been processed but failed. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - PENDING + - SUCCESSFUL + - PARTIAL_SUCCESS + - FAILURE + + StatusChanged: + description: | + The current status of PENDING can be changed to SUCCESSFUL or PARTIAL_SUCCESS or FAILURE. + In some situations (rare situations) a SUCCESSFUL booking or a device assignment may turn into a FAILURE because of natural disasters, catastrophic events, or for a unknown reason. + In such a situations 'statusInfo' may provide additional information about the reason for the unavailability + type: string + enum: + - SUCCESSFUL + - PARTIAL_SUCCESS + - FAILURE + + BookingStatusInfo: + description: | + This schema provides a detailed status of a booking request + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the QoS Booking for unknown reasons + * `DELETE_REQUESTED`- User requested the deletion of the QoS Booking + * `VALIDATION_PENDING` - The validation is pending. The end user will get a callback with the availability of the booking + * `SERVICE_NOT_AVAILABLE` - The requested booking could not be fulfilled because of operator could not support the service area/number of devices/qosProfile in the requested time + * `QOS_PROFILE_NOT_SUPPORTED` - The requested QoS Profile is not supported by the operator + * `BOOKING_UNKNOWN_ERROR` - An unknown error happened while booking + * `BOOKING_ACCEPTED` - The requested booking is completed successfully. + * `BOOKING_CANCELLED` - The given bookingId was cancelled by the user and is no more valid. + * `BOOKING_EXPIRED` - Booking schedule ended, and the given bookingId is expired and is no more valid + * `BOOKING_ACTIVATED` - Booking schedule started and the booking is activated. + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + - VALIDATION_PENDING + - SERVICE_NOT_AVAILABLE + - QOS_PROFILE_NOT_SUPPORTED + - BOOKING_UNKNOWN_ERROR + - BOOKING_ACCEPTED + - BOOKING_CANCELLED + - BOOKING_EXPIRED + - BOOKING_ACTIVATED + + AssignmentStatusInfo: + description: | + This schema provides a detailed status of an assignment request + * `DEVICE_NOT_FOUND` - One or some of the devices are not found to validate and associate to booking. + * `DEVICE_UNKNOWN_ERROR` - One, or more, or all of devices are not assigned or not released because of unknown error. + * `DEVICE_DISCLOSURE_POLICY_APPLIED` - Some or all of the devices are not disclosed because of privacy, or legal requirements, or for unknown reasons. + * `QUOTA_EXCEEDED` - The number of devices requested to assign to a booking is more than the allocated total for the booking. Only remaining devices are assigned + * `VALIDATION_PENDING` - The device assignment request is pending for validation and verification + * `ASSIGNMENT_COMPLETED` - The request assignment of devices is successfully completed + * `BOOKING_INVALID` - The user requests to release a device from booking, but the booking is invalid + * `BOOKING_CANCELLED` - The user requests to release a device from booking, but the booking is cancelled + * `BOOKING_EXPIRED` - The user requests to release a device from booking, but the booking is expired and no more active + * `BOOKING_TERMINATED` - For unknown reasons booking is terminated by the operator. A booking callback may be issued. + * `RELEASE_PENDING` - Release of requested devices is currently in progress. Some might have already been released, and some are still being processed. + + type: string + enum: + - DEVICE_NOT_FOUND + - DEVICE_UNKNOWN_ERROR + - DEVICE_DISCLOSURE_POLICY_APPLIED + - QUOTA_EXCEEDED + - VALIDATION_PENDING + - ASSIGNMENT_COMPLETED + - BOOKING_INVALID + - BOOKING_CANCELLED + - BOOKING_EXPIRED + - BOOKING_TERMINATED + - RELEASE_PENDING + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + DeviceCount: + description: | + Number of devices that may be assigned to the booking. + type: integer + default: 1 + + RemainingDeviceCount: + description: | + Number of devices that are remaining in the current booking. + type: integer + minimum: 0 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateBookingOrAssign400: + description: Bad Request when creating a QoS booking or assigning devices to a booking. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QOS_BOOKING.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QOS_BOOKING.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + BookingConflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing booking for the same device. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + BOOKING_INPUT_1: + summary: Booking Request Example-1 + description: This is an example of a booking request. + value: + numDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + BOOKING_INPUT_2: + summary: Booking Request Example-2 + description: This is an example of a booking request. + value: + numDevices: 27 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "POLYGON" + boundary: + [ + [-122.406558, 37.789172], + [-122.396558, 37.789172], + [-122.396558, 37.779172], + [-122.406558, 37.779172] + ] + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + + BOOKING_SUCCESSFUL: + summary: Booking Successful + description: QoS Booking is successful and valid `bookingId` is returned along with other input parameters. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACCEPTED" + + BOOKING_FAILURE: + summary: Booking Failed + description: QoS Booking failed, `statusInfo` has additional info. No `bookingId` will be returned. + value: + totalDevices: 0 + remainingDevices: 0 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "FAILURE" + statusInfo: "SERVICE_NOT_AVAILABLE" + + BOOKING_PENDING: + summary: Booking Pending + description: QoS Booking request is pending, `statusInfo` has additional info. No `bookingId` will be returned. + value: + totalDevices: 0 + remainingDevices: 0 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + + BOOKING_RETRIEVED: + summary: Retrieve Booking + description: Retrieve booking information from its `bookingId`. `statusInfo` will provide the current status of the booking. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACTIVATED" + + BOOKING_CANCELLED: + summary: Cancel an existing booking + description: Delete a booking using a valid `bookingId`. Delete operation is successful. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_CANCELLED" + + CANCELLATION_PENDING: + summary: Cancellation is Requested + description: Delete a booking using a valid `bookingId`. Delete operation is pending as operator may need more time to process the request. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 7 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "DELETE_REQUESTED" + + ASSIGNMENT_INPUT_1: + summary: Assignment Input - All Identifiers + description: Assignment Input example. To demonstrate, four devices are used, each with a different type of device identifiers. + value: + devices: + - phoneNumber: "+14145550101" + - networkAccessIdentifier: "+123456789@domain.com" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + - ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + ASSIGNMENT_INPUT_2: + summary: Assignment Input - Phone Number only + description: Assignment Input example. To demonstrate, two devices are used, each device is identified with a phone number. + value: + devices: + - phoneNumber: "+14145550101" + - phoneNumber: "+14145550202" + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + ASSIGNMENT_SUCCESSFUL: + summary: Assignment Successful + description: Assignment is successful and all requested devices were successfully assigned to the given booking. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 11 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - networkAccessIdentifier: "+123456789@domain.com" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + - ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_PARTIAL_SUCCESS: + summary: Assignment Partially Successful + description: Assignment is successful and some but not all of the requested devices are assigned. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + status: "PARTIAL_SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_PENDING: + summary: Assignment Pending + description: Assignment request is still being processed. None of the requested devices are assigned. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + + ASSIGNMENT_FAILURE_1: + summary: Assignment Failed + description: Assignment request failed. Booking is still valid. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "FAILURE" + statusInfo: "QUOTA_EXCEEDED" + + ASSIGNMENT_FAILURE_2: + summary: Assignment Failed for unknown booking information + description: Assignment request failed. Provided `bookingId` is correctly formed but not available. In such a situation, value contains only `status` and `statusInfo`. + value: + status: "FAILURE" + statusInfo: "BOOKING_INVALID" + + ASSIGNMENT_RELEASE_INPUT: + summary: Assignment Release Input + description: This is an example of a device that needs to be released from the given booking. + value: + devices: + - phoneNumber: "+14145550101" + + ASSIGNMENT_RELEASED: + summary: Assignment released successfully + description: Assignment is cancelled successfully and the requested devices are released from booking. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 14 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_RELEASE_PENDING: + summary: Release is pending for requested devices + description: Release of requested devices is currently in progress. Some might have already been released, and some are still being processed. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 14 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + status: "PENDING" + statusInfo: "RELEASE_PENDING" + + ASSIGNMENT_RETRIEVED_1: + summary: Retrieve successful + description: Successfully retrieved assigned devices. All devices are visible in this particular case. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - phoneNumber: "+14145550202" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_RETRIEVED_2: + summary: Retrieve successful - No device details + description: Successfully retrieved assigned devices. Device details are not visible because of policy restrictions. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "DEVICE_DISCLOSURE_POLICY_APPLIED" + + RETRIEVE_BOOKINGS_INPUT: + summary: Input to Retrieve Bookings + description: This is an example of a device that is given as input to Retrieve Bookings + value: + device: + phoneNumber: "+14145550101" + + RETRIEVE_BOOKINGS_ONE_ITEM: + summary: Retrieve successful + description: Successfully retrieved assigned bookings for a given device. The device is part of only one booking. + value: + - bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACCEPTED" + + RETRIEVE_BOOKINGS_NO_ITEMS: + summary: No bookings found for the device + description: No bookings are found for the device, value contains only empty array + value: [] +``` diff --git a/marked/QoSBooking/code/API_definitions/qos-booking/raw.md b/marked/QoSBooking/code/API_definitions/qos-booking/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e049c5fa1cf93ee8146e8e90732a955825d0f676 --- /dev/null +++ b/marked/QoSBooking/code/API_definitions/qos-booking/raw.md @@ -0,0 +1,1492 @@ +# qos-booking + +```yaml +openapi: 3.0.3 +info: + title: QoS Booking + description: | + The QoS (Quality of Service) Booking API provides programmable interface for developers and other users (capabilities consumers) to request in advance certain network conditions to be provided by Telco networks, without the necessity to have an in-depth knowledge of the underlying network complexity (e.g. the 4G/5G system in case of a mobile network). + + The API enables API consumers to book the assignment of a predefined QoS profile to a specific device, with some conditions such as the start time, duration and location. + + + # Relevant terms and definitions + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the network operator for the device, at the request time. After the booking request is accepted, the device may get different IP addresses, but the booking will still apply to the device that was identified during the request process. Note: Network Access Identifier is defined for future use and will not be supported with v0.1 of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (e.g. duration expiration) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # Resources and Operations overview + The API defines four operations: + + - An operation to setup a new QoS Booking for a given device. + - An operation to get the information about a specific QoS Booking, identified by its `BookingId`. + - An operation to get the QoS Booking for a given device. + - An operation to terminate a QoS Booking, identified by its `BookingId`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS booking in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/QoSBooking + +servers: + - url: "{apiRoot}/qos-booking/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device QoS Booking + description: Manage the booking of QoS + +paths: + /device-qos-bookings: + post: + tags: + - Device QoS Booking + summary: Sets a new booking of QoS for a device + description: | + Triggers a new booking to assign certain QoS Profile to certain device. + + - If the booking is completed synchronously, the response will be 201 with `status` = `SCHEDULED`. + - If the booking request is accepted but not yet completed, the response will be 201 with `status` = `REQUESTED`. + - If the operator determines synchronously that the booking request cannot be fulfilled, the response will be 201 with `status` = `UNAVAILABLE`. + + - If the request includes a notification callback, the client will receive a `status-changed` event with the outcome of the process. The event will be sent also for synchronous operations. + + **NOTES:** + - When the booking status becomes `UNAVAILABLE`, the QoS Booking resource is not immediately released, but will get deleted automatically, at earliest 360 seconds after. + + This behavior allows clients which are not receiving notification events but are polling, to get the booking status information. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createBooking + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBooking" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Booking notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Booking change related event occurs. + Currently only `BOOKING_STATUS_CHANGED` event is defined. + operationId: postBookingNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + BOOKING_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/BOOKING_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Booking created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE" + BOOKING_UNAVAILABLE: + $ref: "#/components/examples/BOOKING_UNAVAILABLE" + "400": + $ref: "#/components/responses/CreateBooking400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/BookingUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:create" + + /device-qos-bookings/{bookingId}: + get: + tags: + - Device QoS Booking + summary: Get QoS Booking information + description: | + Querying for QoS Booking information details + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. + - The QoS Booking must have been created by the same API client given in the access token. + + operationId: getBookingById + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE" + BOOKING_UNAVAILABLE: + $ref: "#/components/examples/BOOKING_UNAVAILABLE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:read" + + delete: + tags: + - Device QoS Booking + summary: Deletes a QoS Booking + description: | + Release resources related to a QoS Booking. + + If the notification callback is provided and the booking status was `SCHEDULED` or `AVAILABLE`, when the deletion is completed, the client will receive, in addition to the response, a `BOOKING_STATUS_CHANGED` event with + - `status` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `status` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. + - The QoS Booking must have been created by the same API client given in the access token. + operationId: deleteBooking + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Booking deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `SCHEDULED` or `AVAILABLE` with `statusInfo` set to `DELETE_REQUESTED`. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:delete" + + /retrieve-device-qos-bookings: + post: + tags: + - Device QoS Booking + summary: Gets the QoS Booking for a device + description: | + Querying for QoS Booking resource information details for a device. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The QoS Booking must have been created by the same API client given in the access token. + - If no QoS booking is found for the requested device, an empty array is returned. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + + operationId: retrieveBookingByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve a booking by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingByDevice" + required: true + responses: + "200": + description: Returns the QoS booking information for a given device. A device may have multiple bookings (for several times and locations), thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingsOutput" + examples: + RETRIEVE_BOOKINGS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_ONE_ITEM" + RETRIEVE_BOOKINGS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_NO_ITEMS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:retrieve-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + BookingId: + name: bookingId + in: path + description: Booking ID that was obtained from the createBooking operation + required: true + schema: + $ref: "#/components/schemas/BookingId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + BookingId: + description: Booking Identifier in UUID format + type: string + format: uuid + + BaseBookingInfo: + description: Common attributes of a QoS Booking + type: object + properties: + qosProfile: + $ref: "#/components/schemas/QosProfileName" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + devicePorts: + description: The ports used locally by the device for flows to which the requested QoS profile should apply. If omitted, then the qosProfile will apply to all flows between the device and the specified application server address and ports + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationServerPorts: + description: A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + + BookingInfo: + description: | + Booking related information returned in responses. + Optional device object only to be returned if provided in createBooking. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in createBooking). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time of QoS Booking creation. + allOf: + - $ref: "#/components/schemas/BaseBookingInfo" + - type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + startTime: + description: Date and time when QoS profile is scheduled to become available. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + duration: + description: | + Session duration in seconds. Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + - When `qosStatus` is "REQUESTED" or "SCHEDULED", the value is the duration to be scheduled, granted by the implementation. + - When `qosStatus` is "AVAILABLE", the value is the overall duration since `startedAt`. + - When `qosStatus` is "UNAVAILABLE", the value is the overall effective duration since `startedAt` until the session was terminated. + type: integer + format: int32 + minimum: 1 + serviceArea: + $ref: "#/components/schemas/Area" + bookingId: + $ref: "#/components/schemas/BookingId" + startedAt: + description: Date and time when the Booking became "AVAILABLE". Not to be returned when `status` is "REQUESTED" or "SCHEDULED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - bookingId + - status + - startTime + - duration + - serviceArea + + CreateBooking: + description: Attributes to request a new QoS Booking + allOf: + - $ref: "#/components/schemas/BaseBookingInfo" + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + startTime: + description: Date and time when the API consumer requests the QoS profile to become available. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + duration: + description: + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + type: integer + format: int32 + minimum: 1 + serviceArea: + $ref: "#/components/schemas/Area" + required: + - startTime + - duration + - serviceArea + + RetrieveBookingByDevice: + description: Attributes to look for QoS Booking + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveBookingsOutput: + description: QoS bookings for a given device + type: array + items: + $ref: "#/components/schemas/BookingInfo" + minItems: 0 + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the [QoS Profile API](link TBC). + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-booking.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-booking.v0.status-changed: "#/components/schemas/EventStatusChanged" + + EventStatusChanged: + description: Event to notify a QoS Booking status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - bookingId + - status + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `status`. Currently `statusInfo` is only applicable when `status` is 'UNAVAILABLE'. + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the QoS Booking + * `DELETE_REQUESTED`- User requested the deletion of the QoS Booking + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + AREANAME: "#/components/schemas/AreaName" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + AREANAME - The area is defined as an area name. + enum: + - CIRCLE + - POLYGON + - AREANAME + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + AreaName: + description: The value of "AreaName" might be predefined and only regional or even an operator-specific in this API version. As a prerequisite, the API Provider may offer API Consumer the "AreaName" values, which API consumer can request, in a preparation phase. And then API Consumers can select from the "AreaNames" as Service Areas. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - areaName + properties: + areaName: + type: string + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to clients. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + ApplicationServerIpv4Address: + type: string + example: "198.51.100.0/24" + description: | + IPv4 address may be specified in form
                      as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                      as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Status: + description: | + The current status of the requested QoS Booking. The status can be one of the following: + * `REQUESTED` - QoS booking has been requested but is still being processed. + * `SCHEDULED` - QoS booking has been granted for a future start time. + * `AVAILABLE` - The requested QoS profile has been activated for the device. + * `UNAVAILABLE` - The QoS booking request has been processed but is not scheduled or active. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - REQUESTED + - SCHEDULED + - AVAILABLE + - UNAVAILABLE + + StatusChanged: + description: | + The current status of a requested, scheduled or previously available QoS Booking. Applicable values in the event are: + * `SCHEDULED` - QoS booking has been granted for a future start time. + * `AVAILABLE` - The requested QoS profile has been activated for the device. + * `UNAVAILABLE` - The QoS booking request has been processed but is not scheduled or active. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - SCHEDULED + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateBooking400: + description: Bad Request when creating a QoS booking. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QOS_BOOKING.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QOS_BOOKING.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + BookingConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing booking for the same device. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + BookingUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QOS_BOOKING.NOT_MANAGED_AREA_TYPE + - QOS_BOOKING.AREA_NOT_COVERED + - QOS_BOOKING.INVALID_AREA + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QOS_BOOKING_422_NOT_MANAGED_AREA_TYPE: + summary: Not managed area type + description: The requested area type is currently not supported by implementation + value: + status: 422 + code: QOS_BOOKING.NOT_MANAGED_AREA_TYPE + message: "The requested area type is not managed" + QOS_BOOKING_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: QOS_BOOKING.AREA_NOT_COVERED + message: "Unable to cover the requested area" + QOS_BOOKING_422_INVALID_AREA: + summary: Invalid area + description: The requested area value is not valid for the system. Details to be provided in the message. + value: + status: 422 + code: QOS_BOOKING.INVALID_AREA + message: "The requested area is too small" + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + summary: QoS booking status is available, with device included in response + description: QoS booking info when status is available, and request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + qosProfile: "QOS_L" + sink: "https://application-server.com/notifications" + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + startTime: "2024-06-01T12:00:00Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "AVAILABLE" + + BOOKING_UNAVAILABLE: + summary: QoS booking is unavailable, with device not included in response + description: QoS booking info when status is unavailable due to network termination. Request used a 3-legged access token, or possibly a single device identifier + value: + qosProfile: "Acme2" + sink: "https://application-server.com/notifications" + startTime: "2024-06-01T12:00:00Z" + duration: 2428 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "UNAVAILABLE" + statusInfo: "NETWORK_TERMINATED" + + BOOKING_STATUS_CHANGED_EXAMPLE: + summary: Booking status changed + description: Cloud event example for status change to UNAVAILABLE due to DURATION_EXPIRED + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://api.example.com/qod/v1/sessions/123e4567-e89b-12d3-a456-426614174000" + type: "org.camaraproject.qos-booking.v0.status-changed" + specversion: "1.0" + time: "2024-06-01T13:00:00Z" + data: + bookingId: "123e4567-e89b-12d3-a456-426614174000" + status: "UNAVAILABLE" + statusInfo: "DURATION_EXPIRED" + + RETRIEVE_BOOKINGS_ONE_ITEM: + summary: List of QoS sessions for the device + description: A single QoS session for the device is available + value: + - qosProfile: "QOS_L" + applicationServer: + ipv4Address: "0.0.0.0/0" + sink: "https://application-server.com/notifications" + device: + phoneNumber: "+123456789" + startTime: "2024-06-01T12:00:00Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "AVAILABLE" + + RETRIEVE_BOOKINGS_NO_ITEMS: + summary: No bookings found for the device + description: An empty array is returned when no bookings are found for the device + value: [] +``` diff --git a/marked/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist/raw.md b/marked/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aad6525265a28a5873f6e624e7481d275de56645 --- /dev/null +++ b/marked/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qos-booking v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/qos-booking.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/qos-booking.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/3YPVB) | diff --git a/marked/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist/raw.md b/marked/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5694767280af442e706bc08d368d0e839d12e782 --- /dev/null +++ b/marked/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qos-booking-and-assignment v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                      public | stable
                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/qos-booking-and-assignment.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](code/Test_definitions/qos-booking-and-assignment.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IYA5Cg) | diff --git a/marked/QoSBooking/documentation/SupportingDocuments/README/raw.md b/marked/QoSBooking/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/QoSBooking/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/QualityOnDemand/README/raw.md b/marked/QualityOnDemand/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc2e2dda3023f69c9f95d34ade196a4301a7a684 --- /dev/null +++ b/marked/QualityOnDemand/README/raw.md @@ -0,0 +1,65 @@ + + + + + + + + + +# QualityOnDemand + +Incubating API Repository to evolve and maintain the definitions and documentation of QualityOnDemand Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/hAClB) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) + +## Scope + +* Service APIs for “Quality on Demand” (see APIBacklog.md) +* The Service APIs provide the API consumer with the ability to: + * retrieve the possible quality options (profiles) from the network (qos-profiles) + * set the quality for a connection of a mobile device or a home device within the access network + * dynamically, for a selected session of a specific duration (quality-on-demand) + * provisioned, applying the same quality each time the device connects to the network (qod-provisioning) + * get a notification if the network cannot fulfill the requested quality profile (quality-on-demand, qod-provisioning) +* Describe, develop, document and test the APIs (with 1–2 Service Providers) +* Started: October 2021 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/QualityOnDemand/releases/tag/r3.2) (Fall25), with the following API versions: + * **qos-profiles v1.1.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/qos-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-profiles.yaml) + * **qos-provisioning v0.3.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/qos-provisioning.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-provisioning.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-provisioning.yaml) + * **quality-on-demand v1.1.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/quality-on-demand.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/quality-on-demand.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/quality-on-demand.yaml) +* The latest public release is always available here: https://github.com/camaraproject/QualityOnDemand/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/QualityOnDemand/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/QualityOnDemand/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Friday, 13:00 UTC (14:00 CET, 15:00 CEST). For date/time of the next meeting, see previous meeting minutes + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94112812156?password=f238d6af-c959-48d7-a862-abdb3c648e40) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) +* Mailing List + * Subscribe / unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/QualityOnDemand/code/API_definitions/qos-profiles/raw.md b/marked/QualityOnDemand/code/API_definitions/qos-profiles/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1e29843de2978bd8a122078708b6d3501098e233 --- /dev/null +++ b/marked/QualityOnDemand/code/API_definitions/qos-profiles/raw.md @@ -0,0 +1,856 @@ +# qos-profiles + +```yaml +openapi: 3.0.3 +info: + title: QoS Profiles + description: | + The Quality-of-Service (QoS) Profiles API provides a set of predefined network performance characteristics, such as latency, throughput, and priority, identified by a unique name. These profiles allow application developers to specify the desired network behavior for their application's data traffic, ensuring optimal performance. By selecting an appropriate QoS profile, developers can request stable latency (reduced jitter) or throughput for specific data flows between client devices and application servers when used by the Quality-On-Demand APIs. + + # Introduction + + QoS Profiles are used in conjunction with other Quality-On-Demand APIs, to offer the API consumer the capability to request for stable latency (reduced jitter) or throughput for some specified application data flows between application clients (within a user device) and Application Servers (backend services). The API consumer has a pre-defined set of Quality of Service (QoS) profiles which they could choose from depending on their latency or throughput requirements. The QoS profiles are defined by the API provider and are mapped to the connectivity characteristics of the supported networks. + + # API functionality + + The QoS Profiles API provides the following functionality: + - Discover all QoS profiles offered by the API provider + - Discover the available QoS profiles for a specific device + - Retrieve the characteristics of a specific QoS profile by name + + How QoS profiles are mapped to connectivity characteristics are subject to agreements between the API provider and the API consumer. Within the CAMARA project, you can find a sample for such a mapping of QoS profiles. [CAMARA QoS Profiles Mapping Table (REFERENCE DRAFT)](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoSProfile_Mapping_Table.md) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + The two operations defined by this API (`getQosProfile` and `retrieveQoSProfiles`) both allow the API consumer to use a three-legged access token to specify a target device as a query filter. When provided, only profiles available to the specified target device will be returned. Additionally, when a two-legged access token is used, the operation `retrieveQoSProfiles` allows the API consumer to optionally specify the target device in the request body. + + Hence, for the `retrieveQoSProfiles` operation: + - When invoked using a two-legged access token, the optional input device object will be used as filter if present. + + - When invoked using a three-legged access token, this optional identifier in the request body MUST NOT be provided, as the device to filter will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the device can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify a single device from that phone number. When filtering QoS profiles by device in such scenarios, one of the following options should be used: + - Use the authorisation code flow to obtain a 3-legged access token, which will automatically identify the intended device + - Identify the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/qos-profiles/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: QoS Profiles + description: Manage QoS Profiles + +paths: + /retrieve-qos-profiles: + post: + tags: + - QoS Profiles + summary: Retrieve QoS profiles + description: | + Returns all QoS Profiles that match the given criteria. + **NOTES:** + - The access token may be either a 2-legged or 3-legged access token. + - If the access token is 3-legged, all returned QoS Profiles will be available to the subject (device) associated with the access token. + - If the access token is 2-legged and a device filter is provided, all returned QoS Profiles will be available to that device. If multiple device identifiers are provided within the device property, only QoS Profiles available to the device identifier chosen by the implementation will be returned, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. Additionally, this call may include complex data structures. + [CAMARA API Design Guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/API-design-guidelines.md#post-or-get-for-transferring-sensitive-or-complex-data) + + security: + - openId: + - qos-profiles:read + operationId: retrieveQoSProfiles + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to query QoS Profiles for a given device + content: + application/json: + schema: + $ref: "#/components/schemas/QosProfileDeviceRequest" + required: true + responses: + "200": + description: Contains information about QoS Profiles + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/QosProfile" + examples: + List of QoS Profiles: + $ref: "#/components/examples/LIST_OF_QOS_PROFILES" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /qos-profiles/{name}: + get: + tags: + - QoS Profiles + summary: "Get QoS Profile for a given name" + operationId: getQosProfile + description: | + Returns a QoS Profile that matches the given name. + + The access token may be either a 2-legged or 3-legged access token. If the access token is 3-legged, a QoS Profile is only returned if available to all subjects associated with the access token. + + security: + - openId: + - qos-profiles:read + parameters: + - name: name + in: path + description: Qos Profile name + required: true + schema: + $ref: "#/components/schemas/QosProfileName" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about QoS Profiles + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/QosProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + QosProfile: + description: | + Data type with attributes of a QosProfile + type: object + properties: + name: + $ref: "#/components/schemas/QosProfileName" + description: + description: | + A description of the QoS profile. + type: string + example: "QoS profile for video streaming" + status: + $ref: "#/components/schemas/QosProfileStatusEnum" + countryAvailability: + description: | + A list of countries, and optionally networks, for which the API provider makes the profile available. + - When profiles are filtered for a specific device (i.e. using a 3-legged access token or an explicit device filter parameter), the profile can be used by that device in any of these countries when connected to any of the listed networks (assuming roaming is permitted for networks that are not the device's home network), or the API provider's own network if no networks are listed + - When there is no device filter, availability for a given country means that the QoS profile may be available to some devices connected to the listed networks in that country (or to the API provider’s default network if none are listed). However, this does not imply that the profile is available to all devices, or that a particular device will be able to use the profile across all listed countries or networks. In particular, the response does not provide enough information to determine availability for roaming for specific devices; consumers should query the API with a specific device identifier to get definitive availability. + - If this field is not present in the QoS profile, no assumption can be made about the availability of the profile in any given country or for any given network + allOf: + - $ref: "#/components/schemas/Availability" + targetMinUpstreamRate: + description: | + This is the target minimum upload speed for the QoS profile. + It represents the minimum rate that the network attempts to deliver. + Please note that this is a target value—the network might not always be able to provide this rate under all conditions. + It helps ensure that applications like video calls or live streaming perform consistently. + allOf: + - $ref: "#/components/schemas/Rate" + maxUpstreamRate: + description: | + The maximum best effort data + allOf: + - $ref: "#/components/schemas/Rate" + maxUpstreamBurstRate: + description: | + When defined, this is the maximum upstream burst rate for the QoS profile, that will enable + the network to burst data at a higher rate than the maxUpstreamRate for a period of time. + allOf: + - $ref: "#/components/schemas/Rate" + targetMinDownstreamRate: + description: | + This is the target minimum download speed for the QoS profile. + It represents the minimum rate that the network attempts to deliver. + Please note that this is a target value—the network might not always be able to provide this rate under all conditions. + It helps ensure that applications like video calls or live streaming perform consistently. + allOf: + - $ref: "#/components/schemas/Rate" + maxDownstreamRate: + description: | + The maximum best effort rate + allOf: + - $ref: "#/components/schemas/Rate" + maxDownstreamBurstRate: + description: | + When defined, this is the maximum downstream burst rate for the QoS profile, that will enable + the network to burst data at a higher rate than the maxDownstreamRate for a period of time. + This can result in improved user experience when there is additional network capacity. + For instance, when a user is streaming a video, the network can burst data at a higher rate + to fill the buffer, and then return to the maxUpstreamRate once the buffer is full. + allOf: + - $ref: "#/components/schemas/Rate" + minDuration: + description: | + The shortest time period that this profile can be deployed. + allOf: + - $ref: "#/components/schemas/Duration" + maxDuration: + description: | + The maximum time period that this profile can be deployed. + Overall session duration must not exceed this value. This includes the initial requested duration plus any extensions. + allOf: + - $ref: "#/components/schemas/Duration" + priority: + type: integer + example: 20 + description: | + Priority levels allow efficient resource allocation and ensure optimal performance + for various services in each technology, with the highest priority traffic receiving + preferential treatment. + The lower value the higher priority. + Not all access networks use the same priority range, so this priority will be + scaled to the access network's priority range. + format: int32 + minimum: 1 + maximum: 100 + packetDelayBudget: + description: | + The packet delay budget is the maximum allowable one-way latency between the customer's device + and the gateway from the operator's network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, such as voice calls, + video streaming, and data. + The end-to-end or round trip latency will be about two times this value plus the latency not controlled + by the operator + allOf: + - $ref: "#/components/schemas/Duration" + jitter: + description: | + The jitter requirement aims to limit the maximum variation in round-trip + packet delay for the 99th percentile of traffic, following ITU Y.1540 + standards. It considers only acknowledged packets in a session, which are + packets that receive a confirmation of receipt from the recipient (e.g., + using TCP). This requirement helps maintain consistent latency, essential + for real-time applications such as VoIP, video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + packetErrorLossRate: + type: integer + description: | + This field specifies the acceptable level of data loss during transmission. + The value is an exponent of 10, so a value of 3 means that up to 10⁻³, or 0.1%, of the + data packets may be lost. This setting is part of a broader system that categorizes + different types of network traffic (like phone calls, video streams, or data transfers) + to ensure they perform reliably on the network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + l4sQueueType: + type: string + enum: + - non-l4s-queue + - l4s-queue + - mixed-queue + description: | + + **NOTE**: l4sQueueType is experimental and could change or be removed in a future release. + + Specifies the type of queue for L4S (Low Latency, Low Loss, Scalable Throughput) traffic management. L4S is an advanced queue management approach designed to provide ultra-low latency and high throughput for internet traffic, particularly beneficial for interactive applications such as gaming, video conferencing, and virtual reality. + + **Queue Type Descriptions:** + + - **non-l4s-queue**: + A traditional queue used for legacy internet traffic that does not utilize L4S enhancements. It provides standard latency and throughput levels. + + - **l4s-queue**: + A dedicated queue optimized for L4S traffic, delivering ultra-low latency, low loss, and scalable throughput to support latency-sensitive applications. + + - **mixed-queue**: + A shared queue that can handle both L4S and traditional traffic, offering a balance between ultra-low latency for L4S flows and compatibility with non-L4S flows. + + externalDocs: + description: For more details, refer to the L4S standard. + url: https://datatracker.ietf.org/doc/rfc9330/ + serviceClass: + type: string + description: | + + **NOTE**: serviceClass is experimental and could change or be removed in a future release. + + The name of a Service Class, representing a QoS Profile designed to provide optimized behavior for a specific application type. While DSCP values are commonly associated with Service Classes, their use may vary across network segments and may not be applied throughout the entire end-to-end QoS session. This aligns with the serviceClass concept used in HomeDevicesQoQ for consistent terminology. + + Service classes define specific QoS behaviors that map to DSCP (Differentiated Services Code Point) values or Microsoft QoS traffic types. + + The supported mappings are: + 1. Values aligned with the [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines for differentiated traffic classes. + 2. Microsoft [QOS_TRAFFIC_TYPE](https://learn.microsoft.com/en-us/windows/win32/api/qos2/ne-qos2-qos_traffic_type) values for Windows developers. + + **Supported Service Classes**: + + | Service Class Name | DSCP Name | DSCP value (decimal) | DCSP value (binary) | Microsoft Value | Application Examples | + |-----------------------|-----------|----------------------|---------------------|-----------------|----------------------------------------------------------------------| + | Microsoft Voice | CS7 | 56 | 111000 | 4,5 | Microsoft QOSTrafficTypeVoice and QOSTrafficTypeControl | + | Microsoft Audio/Video | CS5 | 40 | 101000 | 2,3 | Microsoft QOSTrafficTypeExcellentEffort and QOSTrafficTypeAudioVideo | + | Real-Time Interactive | CS4 | 32 | 100000 | | Video conferencing and Interactive gaming | + | Multimedia Streaming | AF31 | 26 | 011010 | | Streaming video and audio on demand | + | Broadcast Video | CS3 | 24 | 011000 | | Broadcast TV & live events | + | Low-Latency Data | AF21 | 18 | 010010 | | Client/server transactions Web-based ordering | + | High-Throughput Data | AF11 | 10 | 001010 | | Store and forward applications | + | Low-Priority Data | CS1 | 8 | 001000 | 1 | Any flow that has no BW assurance - also: | + | | | | | | Microsoft QOSTrafficTypeBackground | + | Standard | DF(CS0) | 0 | 000000 | 0 | Undifferentiated applications - also: | + | | | | | | Microsoft QOSTrafficTypeBestEffort | + enum: + - microsoft_voice # Microsoft QOSTrafficTypeVoice or Control + - microsoft_audio_video # Microsoft QOSTrafficTypeExcellentEffort or AudioVideo + - real_time_interactive # Video conferencing and interactive gaming + - multimedia_streaming # Streaming video or audio on demand + - broadcast_video # Broadcast TV and live events + - low_latency_data # Client/server transactions Web-based ordering + - high_throughput_data # STore and forward applications + - low_priority_data # Low-priority background traffic + - standard # Default traffic class + example: real_time_interactive + required: + - name + - status + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profile names like `QOS_E`, `QOS_S`, `QOS_M`, and `QOS_L` + - A searchable descriptive name + type: string + example: voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + Duration: + description: Specification of duration + type: object + properties: + value: + description: Quantity of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + QosProfileStatusEnum: + description: | + The current status of the QoS Profile + - `ACTIVE`- QoS Profile is available to be used + - `INACTIVE`- QoS Profile is not currently available to be deployed + - `DEPRECATED`- QoS profile is actively being used in a QoD session, but can not be deployed in new QoD sessions + type: string + enum: + - ACTIVE + - INACTIVE + - DEPRECATED + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + QosProfileDeviceRequest: + description: | + Request object for QoS Profiles for a given device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + name: + $ref: "#/components/schemas/QosProfileName" + status: + $ref: '#/components/schemas/QosProfileStatusEnum' + + Availability: + description: A list of countries, and optionally networks, for which the API provider makes the profile available + type: array + items: + type: object + required: + - countryName + properties: + countryName: + description: The two letter ISO 3166-2 country code for the country in which the QoS profile is available in at least one network + type: string + pattern: ^[A-Z]{2}$ + example: "GB" + networks: + description: A list of networks within the country for which the QoS profile is available from the API provider + type: array + items: + description: The network identifier. For mobile networks, this is the PLMN Identifier (MCC + MNC), which is a 5 or 6 digit integer. + type: string + example: "23591" + example: ["23591", "23415"] + example: {"countryName": "GB", "networks": ["23591", "23415"]} + example: [{"countryName": "GB", "networks": ["23591", "23415"]}, {"countryName": "DE", "networks": ["26202"]}] + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and the specified application server, unless further restricted by the optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + LIST_OF_QOS_PROFILES: + summary: A list of QoS profiles with a single entry + description: Example response when requesting a list of QoS profiles + value: + - name: "voice" + description: "QoS profile for high-quality interactive voice" + status: "ACTIVE" + targetMinUpstreamRate: + value: 100 + unit: "kbps" + targetMinDownstreamRate: + value: 100 + unit: "kbps" + minDuration: + value: 1 + unit: "Days" + maxDuration: + value: 10 + unit: "Days" + priority: 10 + packetDelayBudget: + value: 50 + unit: "Milliseconds" + jitter: + value: 5 + unit: "Milliseconds" + packetErrorLossRate: 3 + l4sQueueType: "non-l4s-queue" +``` diff --git a/marked/QualityOnDemand/code/API_definitions/qos-provisioning/raw.md b/marked/QualityOnDemand/code/API_definitions/qos-provisioning/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ae258ada43498b3c7a91b498678c4e716562cb41 --- /dev/null +++ b/marked/QualityOnDemand/code/API_definitions/qos-provisioning/raw.md @@ -0,0 +1,1262 @@ +# qos-provisioning + +```yaml +openapi: 3.0.3 +info: + title: QoS Provisioning + description: | + The Quality of Service (QoS) Provisioning API provides a programmable interface for developers to request the indefinite assignment of a specified QoS profile to all traffic being sent or received by a specified device. + + The association resulting from the QoS provisioning request is represented by a QoS assignment record (or QoS assignment for short) that includes information about the date of assignment, the QoS profile assigned to a device, the assignment status, etc., as well as an `assignmentId` that uniquely identifies this record for later use. + + Additionally, this API configures the network to apply the requested QoS profile to a specified device whenever the device is connected to the network, until the assignment is revoked. + + # Relevant terms and definitions + + * **QoS profiles and QoS profile labels**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone Number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the provisioning details. If only a single device identifier is provided, the implementation may or may not include the device identifier in the assignment details. + + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (eg. assignment termination) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. + + # Resources and Operations overview + The API defines four operations: + + - An operation to assign a QoS profile for a given device indefinitely. + - An operation to get the information about a specific QoS assignment record, identified by its `assignmentId`. + - An operation to get the details of a QoS assignment record for a given device. + - An operation to revoke the assignment of a QoS profile to a given device, identified by the `assignmentId`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + - If the requested `qosProfile` exists but is currently not available or incompatible for the QoS assignment (e.g., its status is INACTIVE or DEPRECATED, or its characteristics are not compatible with QoS Provisioning service), then the server will return an error with the `422 QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE` error code. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the QoS profile should apply from that phone number. If the phone number is used as the device identifier when assigning a QoS profile in a multi-SIM scenario, the API may respond with an error, apply the QoS profile to all devices in the multi-SIM group, or apply the QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/qos-provisioning/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: QoS Assignment + description: Manage the permanent assignment of a QoS profile to a device + +paths: + /qos-assignments: + post: + tags: + - QoS Assignment + summary: Triggers the provisioning process for the assignment of a QoS profile to a device + description: | + Initiates the assignment of a specific QoS profile to a given device when connected to the operator's network. + + - If the QoS profile assignment is completed synchronously, the response will be 201 with `status` = `AVAILABLE`. + - If the QoS profile assignment request is accepted but not yet completed, the response will be 201 with `status` = `REQUESTED`. + - If the operator determines synchronously that the QoS profile assignment request cannot be fulfilled, the response will be 201 with `status` = `UNAVAILABLE`. + + - If the request includes the `sink` and `sinkCredential` properties, the client will receive a `status-changed` event with the outcome of the process. The event will be sent also for synchronous operations. + + **NOTES:** + - When the assignment status becomes `UNAVAILABLE`, the QoS profile assignment is not immediately released, but will get deleted automatically, at earliest 360 seconds after. + + This behavior allows API consumers that are not receiving notification events but are polling, to get the QoS profile assignment status information. Before a client can attempt to create a new QoS profile assignment for the same device, they must release the previous assignment resources with an explicit `delete` operation if not yet automatically deleted. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createQosAssignment + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to assign a QoS profile to a device + content: + application/json: + schema: + $ref: "#/components/schemas/CreateAssignment" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Assignment notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The QoS server will call this endpoint whenever any QoS assignment change related event occurs. + Currently only `ASSIGNMENT_STATUS_CHANGED` event is defined. + operationId: postQosAssignmentNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + ASSIGNMENT_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/ASSIGNMENT_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Assignment created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + Successful QoS Profile Assignment Creation: + $ref: "#/components/examples/ASSIGNMENT_CREATION_EXAMPLE" + Successful QoS Profile Assignment Creation with Device in the response: + $ref: "#/components/examples/ASSIGNMENT_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/CreateAssignment400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/AssignmentConflict409" + "422": + $ref: "#/components/responses/CreateAssignment422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:create" + + /qos-assignments/{assignmentId}: + get: + tags: + - QoS Assignment + summary: Get the QoS profile assignment information identified by an assignment record ID + description: | + Querying for details about the QoS profile assignment + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS profile assignment must also be associated with the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + operationId: getQosAssignmentById + parameters: + - $ref: "#/components/parameters/assignmentId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain assignment + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + ASSIGNMENT_AVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE" + ASSIGNMENT_UNAVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_UNAVAILABLE" + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:read" + + delete: + tags: + - QoS Assignment + summary: Revokes a QoS profile assignment identified by an assignment record ID + description: | + Revokes the assignment of a QoS profile to a device performed by a previous assignment operation. + + If the notification callback is provided and the assignment status was `AVAILABLE`, when the process is completed, the API consumer will receive in addition to the response a `ASSIGNMENT_STATUS_CHANGED` event with + - `status` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `status` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS profile assignment must also be associated with the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + operationId: revokeQosAssignment + parameters: + - $ref: "#/components/parameters/assignmentId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Assignment revoked + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `AVAILABLE` with `statusInfo` set to `DELETE_REQUESTED`. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:delete" + + /retrieve-qos-assignment: + post: + tags: + - QoS Assignment + summary: Returns the assignment record details of the QoS profile assignment for a device + description: | + Returns the details of the record for the assignment of a QoS profile to a device, if any. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + - If no QoS profile assignment is found for the device, an error response 404 is returned with code "NOT_FOUND". + - This call uses the POST method instead of GET to comply with the [CAMARA Commonalities guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/CAMARA-API-Design-Guide.md#65-post-or-get-for-transferring-sensitive-or-complex-data) for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + + operationId: getQosAssignmentByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve an assignment record by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveAssignmentByDevice" + required: true + responses: + "200": + description: Returns information about the QoS profile assignment for the device. + + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + ASSIGNMENT_AVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE" + ASSIGNMENT_UNAVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_UNAVAILABLE" + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:read-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + assignmentId: + name: assignmentId + in: path + description: Identifier of the assignment record for the QoS profile assignment, that was created by the `createQosAssignment` operation + required: true + schema: + $ref: "#/components/schemas/AssignmentId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + AssignmentId: + description: Identifier of the assignment record for the QoS profile assignment, that was created by the `createQosAssignment` operation + type: string + format: uuid + + BaseAssignmentInfo: + description: Common attributes of the assignment record for a QoS profile assignment + type: object + properties: + device: + $ref: "#/components/schemas/Device" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + + AssignmentInfo: + description: | + Information about a QoS profile assignment returned in responses. + Optional device object only to be returned if provided in `createQosAssignment`. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in assignQosProfile). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time the QoS profile assignment was created. + + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + - $ref: "#/components/schemas/BaseAssignmentInfo" + - type: object + properties: + assignmentId: + $ref: "#/components/schemas/AssignmentId" + startedAt: + description: Date and time when the QoS profile assignment became "AVAILABLE". Not to be returned when `status` is "REQUESTED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:00Z" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - assignmentId + - status + + CreateAssignment: + description: Attributes to request a new QoS profile assignment + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + - $ref: "#/components/schemas/BaseAssignmentInfo" + + RetrieveAssignmentByDevice: + description: Attributes to look for a QoS profile assignment + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now. + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur + after the termination of the requested assignment, allowing the client to be notified of any changes during the + assignment's existence. If the token expires while the assignment is still active, the client will stop receiving notifications. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an API provider is offering may be retrieved by means of the QoS Profile API (qos-profile) or agreed on onboarding time. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-provisioning.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-provisioning.v0.status-changed: "#/components/schemas/EventStatusChanged" + + EventStatusChanged: + description: Event to notify a QoS provisioning status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - assignmentId + - qosStatus + properties: + assignmentId: + $ref: "#/components/schemas/AssignmentId" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `status`: + * `NETWORK_TERMINATED` - Network terminated the QoS profile assignment + * `DELETE_REQUESTED` - User requested the deletion of the QoS profile assignment + + type: string + enum: + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Status: + description: | + The current status of the requested QoS profile assignment. The status can be one of the following: + * `REQUESTED` - QoS profile assignment has been requested but is still being processed. + * `AVAILABLE` - The requested QoS profile has been assigned to the device, and is active. + * `UNAVAILABLE` - The QoS profile assignment request has been processed but is not active. `statusInfo` may provide additional information about the reason for the unavailability. + enum: + - REQUESTED + - AVAILABLE + - UNAVAILABLE + + StatusChanged: + description: | + The current status of a requested or previously available QoS profile assignment. Applicable values in the event are: + * `AVAILABLE` - The requested QoS profile has been assigned to the device, and is active. + * `UNAVAILABLE` - A requested or previously available QoS profile assignment is now unavailable. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateAssignment400: + description: Bad Request with additional errors for implicit notifications + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + AssignmentConflict409: + description: Assignment conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + ASSIGNMENT_409_CONFLICT: + description: The requested provisioning process conflicts with an existing one + value: + status: 409 + code: CONFLICT + message: There is another existing provisioning for the same device + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token.ç + + CreateAssignment422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QOS_PROVISIONING_422_QOS_PROFILE_NOT_APPLICABLE: + description: The requested QoS Profile exists but cannot be used for the QoS assignment. + value: + status: 422 + code: QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE + message: The requested QoS Profile is not compatible with the QoS Provisioning service. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ASSIGNMENT_CREATION_EXAMPLE: + summary: Successful assignment creation without device in the assignment details + description: Example response after a new QoS profile assignment has been created using a 3-legged access token, or possibly a single device identifier + value: + qosProfile: QOS_L + sink: https://application-server.com/callback + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + status: REQUESTED + + ASSIGNMENT_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful assignment creation with device in the assignment details + description: Example response after a new QoS profile assignment has been created using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + device: + phoneNumber: "+123456789" + qosProfile: QOS_L + sink: https://application-server.com/callback + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + status: REQUESTED + + ASSIGNMENT_AVAILABLE: + summary: QoS assignment status is available with device in the assignment details + description: The QoS profile assignment has become available, and the device to which the assignment applies is included in the assignment details + value: + device: + phoneNumber: "+123456789" + qosProfile: QOS_L + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: AVAILABLE + + ASSIGNMENT_UNAVAILABLE: + summary: QoD provisioning status is unavailable + description: The asssignment could not be created or is not active anymore + value: + qosProfile: QOS_L + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: UNAVAILABLE + statusInfo: NETWORK_TERMINATED + + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + summary: QoS assignment status is available + description: Device is optional in responses and must not be provided if it was not provided in the request + value: + qosProfile: QOS_M + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: AVAILABLE + + ASSIGNMENT_STATUS_CHANGED_EXAMPLE: + description: Assignment status changed + summary: Cloud event example for QoD assignment status change to UNAVAILABLE due to NETWORK_TERMINATED + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: https://api.example.com/qos-provisioning/v0.4/qos-assignments/123e4567-e89b-12d3-a456-426614174000 + specversion: "1.0" + type: org.camaraproject.qos-provisioning.v0.status-changed + time: "2021-12-12T00:00:00Z" + data: + assignmentId: 123e4567-e89b-12d3-a456-426614174000 + status: UNAVAILABLE + statusInfo: NETWORK_TERMINATED +``` diff --git a/marked/QualityOnDemand/code/API_definitions/quality-on-demand/raw.md b/marked/QualityOnDemand/code/API_definitions/quality-on-demand/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eb527da802e46a19b2f54459b1a0e33dab4b49c4 --- /dev/null +++ b/marked/QualityOnDemand/code/API_definitions/quality-on-demand/raw.md @@ -0,0 +1,1612 @@ +# quality-on-demand + +```yaml +openapi: 3.0.3 +info: + title: Quality-On-Demand + description: | + The Quality-On-Demand (QoD) API provides a programmable interface for developers and other users (API consumers) to request stable latency or throughput managed by networks without the necessity to have an in-depth knowledge of the underlying network complexity (e.g. the 4G/5G system in case of a mobile network). + + # Introduction + + Industrial (IoT), VR/Gaming, live video streaming, autonomous driving and many other scenarios demand network communication quality and are sensitive to any change in transmission conditions. Being able to request a stable latency (reduced jitter) or prioritized throughput from the network can improve user experience substantially. + + The QoD API offers the application developers the capability to request for stable latency (reduced jitter) or throughput for some specified application data flows between application clients (within a user device) and application servers (backend services). The developer has a pre-defined set of Quality of Service (QoS) profiles which they could choose from depending on their latency or throughput requirements. + + ![QoD API Overview](https://raw.githubusercontent.com/camaraproject/QualityOnDemand/main/documentation/API_documentation/resources/QoD_latency_overview.PNG) + + The usage of the API is based on QoS session resources, which can be created (based on available QoS profiles), queried and deleted. The deletion of a requested session can be triggered by the API consumer or can be triggered automatically once the QoS session has reached its limit. + + # Relevant terms and definitions + + * **QOD service endpoint**: + The URL pointing to the RESTful resource of the QoD API. + + * **Authentication**: + Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the QoD API. + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that an API provider is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone Number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session details. If only a single device identifier is provided, the implementation may or may not include the device identifier in the session details. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Identifier for the application server**: + IPv4 and/or IPv6 address of the application server (application backend) + + * **App-Flow (between the application client and application server)**: + The precise application data flow the developer wants to prioritize and have stable latency or throughput for. This flow is in the current API version determined by the identified device and the application server. And it can be further elaborated with details such as ports or port-ranges. Future version of the API might allow more detailed flow identification features. + + * **Duration**: + Duration (in seconds) for which the QoS session (between application client and application server) should be created. Limits for session duration can be set by the implementation for the QoS profile. The user may request a termination before its expiration. + + * **Notification URL and token**: + The API consumer may provide a callback URL (`sink`) on which notifications about all status change events (eg. session termination) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. + If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version, `sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # API functionality + + The usage of the QoD API is based on QoS profile classes and parameters which define App-Flows. + Based on the API, QoS session resources can be created, queried, and deleted. Once an offered QoS profile class is requested, application users get a prioritized service with stable latency or throughput even in the case of congestion. The QoD API has the following characteristics: + + * A specified App-Flow is prioritized to ensure stable latency or throughput for that flow. + * The prioritized App-Flow is described by providing information such as device IP address (or other device identifier) & application server IP addresses and port/port-ranges. + * The developer specifies the duration for which they need the prioritized App-flow. + * Stable latency or throughput is requested by selecting from the list of QoS profiles made available by the service provider (e.g. QOS_E) to map latency and throughput requirements. + * The API consumer can optionally also specify callback URL (`sink` param) on which notifications for the session can be sent.
                      + + Following diagram shows the interaction between different components + + ![QoD Management API](https://raw.githubusercontent.com/camaraproject/QualityOnDemand/main/documentation/API_documentation/resources/QoD_details.PNG) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + - If the requested `qosProfile` exists but is currently not available for creating a session (e.g., its status is INACTIVE or DEPRECATED), then the server will return an error with the `422 QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE` error code. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS session in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/quality-on-demand/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: QoS Sessions + description: Manage QoS sessions + +paths: + /sessions: + post: + tags: + - QoS Sessions + summary: Creates a new session + description: | + Create QoS Session to manage latency/throughput priorities + + If the qosStatus in the API response is "AVAILABLE" and a notification callback is provided the API consumer will receive in addition to the response a + `QOS_STATUS_CHANGED` event notification with `qosStatus` as `AVAILABLE`. + + If the `qosStatus` in the API response is `REQUESTED`, the client will receive either + - a `QOS_STATUS_CHANGED` event notification with `qosStatus` as `AVAILABLE` after the network notifies that it has created the requested session, or + - a `QOS_STATUS_CHANGED` event notification with `qosStatus` as `UNAVAILABLE` and `statusInfo` as `NETWORK_TERMINATED` after the network notifies that it has failed to provide the requested session. + + A `QOS_STATUS_CHANGED` event notification with `qosStatus` as `UNAVAILABLE` will also be send if the network terminates the session before the requested duration expired + + **NOTES:** + - In case of a `QOS_STATUS_CHANGED` event with `qosStatus` as `UNAVAILABLE` and `statusInfo` as `NETWORK_TERMINATED` the resources of the QoS session are not directly released, but will get deleted automatically at earliest 360 seconds after the event. + + This behavior allows API consumers which are not receiving notification events but are polling to get the session information with the `qosStatus` `UNAVAILABLE` and `statusInfo` `NETWORK_TERMINATED`. Before a API consumer can attempt to create a new QoD session for the same device and flow period they must release the session resources with an explicit `delete` operation if not yet automatically deleted. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createSession + security: + - openId: + - quality-on-demand:sessions:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new session + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSession" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Session notifications callback + summary: "Session notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS session change (e.g. network termination) related event occurs. + Currently only QOS_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + QOS_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/QOS_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Session created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + Successful Session Creation: + $ref: "#/components/examples/SESSION_CREATION_EXAMPLE" + Successful Session Creation With Device Disambiguation: + $ref: "#/components/examples/SESSION_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/CreateSessionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/SessionInConflict409" + "422": + $ref: "#/components/responses/CreateSessionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}: + get: + tags: + - QoS Sessions + summary: Get QoS session information + description: | + Querying for QoS session resource information details + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the end user (and device) associated with the session must also be associated with the access token. + - The session must have been created by the same API client given in the access token + + operationId: getSession + security: + - openId: + - quality-on-demand:sessions:read + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about active session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + SESSION_AVAILABLE: + $ref: '#/components/examples/SESSION_AVAILABLE_EXAMPLE' + SESSION_UNAVAILABLE: + $ref: '#/components/examples/SESSION_UNAVAILABLE_EXAMPLE' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + delete: + tags: + - QoS Sessions + summary: Delete a QoS session + description: | + Release resources related to QoS session + + If the notification callback is provided and the `qosStatus` of the session was `AVAILABLE` the client will receive in addition to the response a `QOS_STATUS_CHANGED` event with + - `qosStatus` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `qosStatus` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. + - The session must must have been created by the same API consumer given in the access token + + operationId: deleteSession + security: + - openId: + - quality-on-demand:sessions:delete + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Session deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}/extend: + post: + tags: + - QoS Sessions + summary: "Extend the duration of an active session" + description: | + Extend the overall session duration of an active QoS session (with qosStatus = AVAILABLE). + The overall duration of the QoS session, including the additional extended duration, shall not exceed the maximum duration limit fixed for the QoS Profile. If the current duration plus the value of `requestedAdditionalDuration` exceeds the maximum limit, the new overall duration shall be capped to the maximum value allowed. + An example: For a QoS profile limited to a `maxDuration` of 50,000 seconds, a QoD session was originally created with duration 30,000 seconds. Before the session expires, the developer requests to extend the session by another 30,000 seconds: + - Previous duration: 30,000 seconds + - Requested additional duration: 30,000 seconds + - New overall session duration: 50,000 seconds (the maximum allowed) + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. + - The session must must have been created by the same API consumer given in the access token + + operationId: extendQosSessionDuration + security: + - openId: + - quality-on-demand:sessions:update + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to extend the duration of an active session + content: + application/json: + schema: + $ref: "#/components/schemas/ExtendSessionDuration" + required: true + responses: + "200": + description: Contains information about active session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + SESSION_EXTENDED: + $ref: "#/components/examples/SESSION_EXTENDED_EXAMPLE" + SESSION_EXTENDED_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/SESSION_EXTENDED_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/GenericExtendSessionDuration400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/SessionStatusConflict409" + "429": + $ref: "#/components/responses/Generic429" + + /retrieve-sessions: + post: + tags: + - QoS Sessions + summary: Get QoS session information for a device + description: | + Querying for QoS session resource information details for a device + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The session must have been created by the same API consumer given in the access token + - If no QoS session is found for the requested device, an empty array is returned. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + [CAMARA API Design Guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/CAMARA-API-Design-Guide.md#65-post-or-get-for-transferring-sensitive-or-complex-data) + + operationId: retrieveSessionsByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to get QoS session information by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsInput" + required: true + responses: + "200": + description: Returns the QoS sessions information for a given device. A device may have multiple sessions, thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsOutput" + examples: + RETRIEVE_SESSIONS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EXAMPLE" + RETRIEVE_SESSIONS_ONE_ITEM_WITH_DEVICE_DISAMBIGUATION_REQUIRED: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EXAMPLE_WITH_DEVICE_RESPONSE" + RETRIEVE_SESSIONS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EMPTY_EXAMPLE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "quality-on-demand:sessions:retrieve-by-device" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + SessionId: + description: Session ID in UUID format + type: string + format: uuid + + BaseSessionInfo: + description: Common attributes of a QoD session + type: object + properties: + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + devicePorts: + description: The ports used locally by the device for flows to which the requested QoS profile should apply. If omitted, then the qosProfile will apply to all flows between the device and the specified application server address and ports + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationServerPorts: + description: A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events about all status changes of the session (e.g. session termination) shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - applicationServer + - qosProfile + + SessionInfo: + description: | + Session related information returned in responses. + Note that the device object is defined as optional and will only to be returned if provided in createSession. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in createSession). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time of session creation. + allOf: + - type: object + properties: + device: + description: Disambiguates the device to which the session applies when multiple device identifiers were provided + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + - $ref: "#/components/schemas/BaseSessionInfo" + - type: object + properties: + sessionId: + $ref: "#/components/schemas/SessionId" + duration: + description: | + Session duration in seconds. Implementations can grant the requested session duration or set a different duration, based on network policies or conditions. + - When `qosStatus` is "REQUESTED", the value is the duration to be scheduled, granted by the implementation. + - When `qosStatus` is AVAILABLE", the value is the overall duration since `startedAt. When the session is extended, the value is the new overall duration of the session. + - When `qosStatus` is "UNAVAILABLE", the value is the overall effective duration since `startedAt` until the session was terminated. + type: integer + format: int32 + minimum: 1 + example: 3600 + startedAt: + description: Date and time when the QoS status became "AVAILABLE". Not to be returned when `qosStatus` is "REQUESTED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:00Z" + expiresAt: + description: | + Date and time of the QoS session expiration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + - When `qosStatus` is "AVAILABLE", it is the limit time when the session is scheduled to finnish, if not terminated by other means. + - When `qosStatus` is "UNAVAILABLE", it is the time when the session was terminated. + - Not to be returned when `qosStatus` is "REQUESTED". + When the session is extended, the value is the new expiration time of the session. + type: string + format: date-time + example: "2024-06-01T13:00:00Z" + qosStatus: + $ref: "#/components/schemas/QosStatus" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - sessionId + - duration + - qosStatus + + CreateSession: + description: Attributes required to create a session + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + - $ref: "#/components/schemas/BaseSessionInfo" + - type: object + properties: + duration: + description: | + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). Implementations can grant the requested session duration or set a different duration, based on network policies or conditions. + type: integer + format: int32 + minimum: 1 + example: 3600 + required: + - duration + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur + after the termination of the requested session, allowing the client to be notified of any changes during the + sessions's existence. If the token expires while the session is still active, the client will stop receiving notifications. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ExtendSessionDuration: + description: Attributes required to extend the duration of an active session + type: object + properties: + requestedAdditionalDuration: + description: | + Additional duration in seconds to be added to the current session duration. The overall session duration, including extensions, shall not exceed the maximum duration limit for the QoS Profile. + type: integer + format: int32 + minimum: 1 + example: 1800 + required: + - requestedAdditionalDuration + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the API provider implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an API provider is offering may be retrieved by means of the QoS Profile API (qos-profile) or agreed on onboarding time. + type: string + example: voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific provider implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.quality-on-demand.v1.qos-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to Cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.quality-on-demand.v1.qos-status-changed: "#/components/schemas/EventQosStatusChanged" + + EventQosStatusChanged: + description: Event to notify a QoS status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - sessionId + - qosStatus + properties: + sessionId: + $ref: "#/components/schemas/SessionId" + qosStatus: + $ref: "#/components/schemas/EventQosStatus" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `qosStatus`. Currently `statusInfo` is only applicable when `qosStatus` is 'UNAVAILABLE'. + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the session before the requested duration expired + * `DELETE_REQUESTED`- User requested the deletion of the session before the requested duration expired + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Device: + description: | + End-user equipment able to connect to a network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to clients. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and the specified application server, unless further restricted by the optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ApplicationServerIpv4Address: + type: string + example: "198.51.100.0/24" + description: | + IPv4 address may be specified in form
                      as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                      as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + QosStatus: + description: | + The current status of the requested QoS session. The status can be one of the following: + * `REQUESTED` - QoS has been requested by creating a session + * `AVAILABLE` - The requested QoS has been provided by the network + * `UNAVAILABLE` - The requested QoS cannot be provided by the network due to some reason + type: string + enum: + - REQUESTED + - AVAILABLE + - UNAVAILABLE + + EventQosStatus: + description: | + The current status of a requested or previously available session. Applicable values in the event are: + * `AVAILABLE` - The requested QoS has been provided by the network. + * `UNAVAILABLE` - A requested or previously available QoS session is now unavailable. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + RetrieveSessionsInput: + description: Parameters to get QoS session information by device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveSessionsOutput: + description: QoS session information for a given device + type: array + items: + $ref: "#/components/schemas/SessionInfo" + minItems: 0 + + responses: + CreateSessionBadRequest400: + description: Bad Request when creating a session + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + GenericExtendSessionDuration400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: NOTE - this error response cannot be returned by the `/extend` operation and will be removed from the API definition in the next version. + value: + status: 400 + code: QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + SessionInConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing session for the same device. + + SessionStatusConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - QUALITY_ON_DEMAND.SESSION_EXTENSION_NOT_ALLOWED + examples: + SessionExtensionNotAllowed: + description: Session extension is in conflict with current session status + value: + status: 409 + code: QUALITY_ON_DEMAND.SESSION_EXTENSION_NOT_ALLOWED + message: Extending the session duration is not allowed in the current state ({qosStatus}). The session must be in the AVAILABLE state. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + CreateSessionUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QUALITY_ON_DEMAND_422_QOS_PROFILE_NOT_APPLICABLE: + description: The requested QoS Profile exists but cannot be used to create a session. + value: + status: 422 + code: QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE + message: The requested QoS Profile is currently not available for session creation. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + SESSION_CREATION_EXAMPLE: + summary: Successful session creation with device not included in response + description: Example response after a new QoS session has been created using a 3-legged access token, or possibly a single device identifier + value: + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + qosStatus: REQUESTED + + SESSION_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful session creation with device included in response + description: Example response after a new QoS session has been created using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + qosStatus: REQUESTED + + SESSION_AVAILABLE_EXAMPLE: + summary: QoS session status is available + description: QoS session info when status is available + value: + duration: 3600 + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + SESSION_UNAVAILABLE_EXAMPLE: + summary: QoS session is unavailable + description: QoS session info when status is unavailable due to network termination + value: + duration: 2428 + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T12:40:28Z" + qosStatus: UNAVAILABLE + statusInfo: NETWORK_TERMINATED + + QOS_STATUS_CHANGED_EXAMPLE: + summary: QoS status changed + description: Cloud event example for QoS status change to UNAVAILABLE due to DURATION_EXPIRED + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: 'https://api.example.com/qod/v1/sessions/123e4567-e89b-12d3-a456-426614174000' + specversion: '1.0' + type: "org.camaraproject.quality-on-demand.v1.qos-status-changed" + time: '2024-06-01T13:00:00Z' + data: + sessionId: '123e4567-e89b-12d3-a456-426614174000' + qosStatus: 'UNAVAILABLE' + statusInfo: 'DURATION_EXPIRED' + + RETRIEVE_SESSIONS_EXAMPLE: + summary: List of QoS sessions for the specified device + description: A single QoS session for the specified device is available + value: + - applicationServer: + ipv4Address: 0.0.0.0/0 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + RETRIEVE_SESSIONS_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: List of QoS sessions for a specified device with the device in the response + description: A single QoS session for the device is available and the device to which the session applies is included in the response + value: + - device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 0.0.0.0/0 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + SESSION_EXTENDED_EXAMPLE: + summary: Successful session extension with device not included in response + description: Example response after the duration of an active QoS session has been extended using a 3-legged access token, or possibly a single device identifier. The session remains AVAILABLE with updated duration and expiresAt values. + value: + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 5400 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:30:00Z" + qosStatus: AVAILABLE + + SESSION_EXTENDED_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful session extension with device included in response + description: Example response after the duration of an active QoS session has been extended using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier. The session remains AVAILABLE with updated duration and expiresAt values. + value: + device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 5400 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:30:00Z" + qosStatus: AVAILABLE + + RETRIEVE_SESSIONS_EMPTY_EXAMPLE: + summary: No sessions found for the device + description: An empty array is returned when no sessions are found for the device + value: [] +``` diff --git a/marked/QualityOnDemand/documentation/API_documentation/QoD_User_Story/raw.md b/marked/QualityOnDemand/documentation/API_documentation/QoD_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..538294fa97c5669c08b2e2d1d3d5c7a4361e2adf --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/QoD_User_Story/raw.md @@ -0,0 +1,10 @@ +# Quality-On-Demand (QoD) API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service), stable latency and/or stable throughput for a specified App-Flow from a Communication Service Provider (CSP), so that I can ensure better quality of experience for our end users including under network congestion. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:Developer
                      **Actors:** Application service providers, hyperscalers, application developers. This User Story does not explicitly describe consent management and hence end users are not included as Actors.
                      **Scope:** *Order To Activate (OTA)* \- Create/Remove/Get service instance (QoD session resource)\, get notification about the instance (QoD session resource) | +| ***Pre-conditions*** | The preconditions are listed below:
                      1. Customer:Developer is eligible to use the QoD API, i.e. the Customer has successfully subscribed to the QoD API on the platform of an API Provider
                      2. the customer application server has requested and received an access token for the required scopes of the API. Which specific authorization flows are to be used will be determined during onboarding process.
                      3. Optional: the customer application server has requested the list of available QoS Profiles with the qos-profile API (alternatively an upfront agreed QoS profile will be used)| +| ***Activities/Steps*** | **Starts when:** The customer application server makes a POST request to the QoD API to create a new QoD session resource with a specified duration and an available QoS Profile, and optionally registers a callback URL for receiving notification events.
                        **Ends when:** The customer application server makes a DELETE request to the QoD API, or the QoD session resource deletion was triggered automatically either because the set duration has expired or the session was terminated by the network (e.g. due to lack of resources). | +| ***Post-conditions*** | The specified App-Flow was provided stable latency or stable throughput and if callback URL was specified, a QoD session resource termination notification was received at the end. | +| ***Exceptions*** | Several exceptions might occur during the QoD API operations
                        - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                        - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                        - Conflict: Internal configuration policies didn’t allow for operations, e.g. a second QoD session for one device.
                        - Session-not-created: Due to other internal errors, QoS session resource could not be created| diff --git a/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table/raw.md b/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7bd54c1c73a2fb41b40fb9c4a835a76a8977421a --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table/raw.md @@ -0,0 +1,16 @@ +# QoS Profiles Mapping Table (REFERENCE DRAFT) + +Here is one possible example of mapping table from QoS Profiles to provided connectivity characteristics. The intention of the examples is to illustrate the principle usage of the defined QoS Profile labels. It focus on connectivity characteristics in a wide area network usage. + +It is generally assumed that there exists an agreement between the API consumer and the API provider (e.g. a network operator or aggregator), which defines the service levels, conditions and restrictions. The agreement is not further detailed out here. In this sense the table below can be considered only as an example. + +## Example: Considering wide-area network usage. +| QOS Profile labels | Network Service Description | Network Service Constraints | +|----------| --------- | ----------- | +| QOS\_E | Latency stays stable under congestion (throughput up to a certain limit, e.g. 500kbps). The application bitrate should not exceed the limit. | The service is only provided, when the device is located within the geographical area, according to the agreement with the API provider.
                        The access to the network service is restricted to a maximal number of simultaneous session. | +| QOS\_L | The network throughput is prioritized up to certain higher limit (e.g. 20Mbps), or without an explicit limit. At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                        The access to the network service is restricted to a maximal number of simultaneous sessions. | +| QOS\_M | The network throughput is prioritized up to certain medium limit (e.g. 8Mbps). At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                        The access to the network service is restricted to a maximal number of simultaneous sessions. | +| QOS\_S | The network throughput is prioritized up to certain lower limit (e.g. 4Mbps). At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                        The access to the network service is restricted to a maximal number of simultaneous session. | + +**Note:** +The QOS profile labels in the table can be used within Camara for validating the QoD APIs. diff --git a/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story/raw.md b/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d1e1184ee22ac191f2f2a0ccafd6dd547f53ec9b --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story/raw.md @@ -0,0 +1,10 @@ +# Quality-Of-Service-Profile (QoS Profile) User Story + +| **Item** | **Details** | +| ----------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **_Summary_** | As an application developer, I want to be able to query the list of available Quality of Service (QoS) profiles. I can then use use one of the Qos Profiles to start a Quality On Demand (QoD) session with a Communication Service Provider (CSP). The QoS profile contains information regarding network requirements for an application such as stable latency or throughput. | +| **_Roles, Actors and Scope_** | **Roles:** API Consumer:Developer

                        **Actors:** Application service providers, hyperscalers, application developers.

                        **Scope:**
                        • Retrieve a list of available QoS profiles (optionally filter by device)
                        • Get details of a QoS Profile
                        | +| **_Pre-conditions_** | The preconditions are listed below:
                        1. Customer:Developer is eligible to use the QoS Profile API, i.e. the Customer has successfully subscribed to the QoS Profile API on the platform of an API Provider
                        2. The customer application has requested and received an access token for the required scopes of the API. Which specific authorization flows are to be used will be determined during onboarding process.
                        | +| **_Activities/Steps_** | **Starts when:** The customer application either makes a POST to retrieve the list of available QoS Profiles or a GET to see the individual details of a QoS Profile.

                        **Ends when:** When the API Consumer:Developer identifies the QoS Profile to use when creating a QoD session. | +| **_Post-conditions_** | None - this is an immutable API. | +| **_Exceptions_** | Several exceptions might occur during the QoS Profile API operations
                        - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                        - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected). | diff --git a/marked/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist/raw.md b/marked/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cd4df89880c59e2f4a154fb901e64da4e4b0ea18 --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for qos-profiles v1.1.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                        public | stable
                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qos-profiles.yaml](/code/API_definitions/qos-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline within YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/QoSProfile_User_Story.md](/documentation/API_documentation/QoSProfile_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see issue [#492](https://github.com/camaraproject/QualityOnDemand/issues/492) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYCtB) | + +(1) Multiple implementation by other operators of previous versions (source: https://open-gateway.gsma.com/map as of 2025-08-29). + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist/raw.md b/marked/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..56faf225e9227768758e0c92c523e3af8e37acd2 --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist/raw.md @@ -0,0 +1,21 @@ +# API Readiness Checklist + +Checklist for qos-provisioning v0.3.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                        public | stable
                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qos-provisioning.yaml](/code/API_definitions/qos-provisioning.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/FYCtB) | + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist/raw.md b/marked/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8e68dc144cd6015abfebee3aaa90b7d0fe37f189 --- /dev/null +++ b/marked/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist/raw.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for quality-on-demand v1.1.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                        public | stable
                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/quality-on-demand.yaml](/code/API_definitions/quality-on-demand.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/QoD_User_Story.md](/documentation/API_documentation/QoD_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see issue [#493](https://github.com/camaraproject/QualityOnDemand/issues/493) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/9ACqB) | + +(1) Multiple implementation by other operators of previous versions (source: https://open-gateway.gsma.com/map as of 2025-08-29). + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..249383e4bcd10164488f43b1b8ea8e9b24d694a5 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021/raw.md @@ -0,0 +1,31 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 10-Dec-2021 + +## Attendees +- Joseantonio Ordonezlucena (Telefonica) +- Petar Torre (Intel) +- Ali Tizghadam (Telus) +- Toshi WAKAYAMA (KDDI) +- Jan Friman (E///) +- Emil Zhang (E///) +- Joachim Dahlgren (E///) +- Christoph Goertz (MobileEdgex) +- Mariusz Sozanski (DT) +- Felix DSouza (DT) +- Shilpa Padgaonkar (DT) + +## Goals +- Check when to restart meetings next year. +- Go through qod open issues +- Identify additional tasks, prepare upcoming ones + +Item | Description +---- | ---- +WG Meeting Series next year | Should be restarted after the first general alliance meeting planned for next year. Invites will follow +QoD open issue https://github.com/camaraproject/rep_main/issues/15 | E/// will provide an introduction to the 2 proposed specifications in the upcoming WG call and will provide details about additional features offered by the specs. They will also provide recmmendations/proposals if any features could be incorporated in existing APIs. +QoD open issue https://github.com/camaraproject/rep_main/issues/16 | All issues were discussed and clarified. We have following action items from the issue discussions:-
                        • Userstories behind qod apis will be submitted by DT in the userstory template format approved from the commonalities WG
                        • Stable vs guaranteed more details from DT to follow in one of the next calls
                        •The term Appflow might limit further possibilities(UE-UE)flow if the API scope is extended later, but we agree to keep it as is currently and can change it if needed in future. Standard resource document in commonalities WG can address the vocabalary consistency issue.
                        • Subactivity to discuss which notificiations are relevant for the QoD API family. Add your insights here:- https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md
                        • Alternatives requested for "session" 2 suggestions already provided by E/// . Alternatives can be documented here https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Changes.md +QoD open issue https://github.com/camaraproject/rep_main/issues/18 | All issues were discussed and clarified. Some action items for DT:-
                        • Provide details what would differ in future regarding the 2 APIs which drove the decision to split the APIs in two
                        • What happens when consumer needs combination of both?
                        • Can the API be extended to provide the consumer with available profile options? + + + diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b1967b28646a34124a96449535d13dd59891cc77 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021/raw.md @@ -0,0 +1,30 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-Oct-2021 +**Note Taker:** Shilpa Padgaonkar + +## Attendees +- Petar Torre +- Joseantonio Ordonezlucena +- Ali Tizghadam +- Noel Wirzius +- Shilpa Padgaonkar + +## Goals +- Workstream1 Kickoff +- Introductions +- Identify additional tasks, prepare upcoming ones + +## Agenda Items + +Item | Description +---- | ---- +Regular meeting schedule | • Agreed to have bi-weekly calls
                        • Shilpa will send out doodle pool for regular bi-weekly time slots +Contributions| • **Intel**
                        - **Supporting capability NEF (Rel-15) sample code:** Intel Distribution of OpenNESS (requires Intel license) has sample application for Network Exposure Function (summary in , API spec here). With support to integrate above NEF sample code.(eg. provide mock code for subset of NEF features)
                        - **Kubernetes and Telemetry:** (Assuming use of Kubernetes) Activate Kubernetes features useful for optimal workload placement (CPU Mgr…), and possibly platform telemetry supporting “to get notification if network cannot fulfill”.  (eg. Scheduling, notifications specific contributions)
                        - **e2e performance characterization:** If during the integration of such API, exposure gateway, NFs… you plan to do performance characterization, we might help with people experienced in similar characterization focusing on edge workloads. (eg. testing framworks, tools, testcases)
                        - **Documenting API design principles:** Contribute text on API design principles like “must Encapsulate; should be Declarative”, with Terminology/Glossary as needed. 

                        • **Telefonica**
                        - Define userstories and usecases
                        - Analyse set of existing APIs and capabilities and how to enrich them
                        - Offer to validate the APIs contributed to the project by using a self built validation tool
                        - Test cases 

                        • **Telus**
                        - Offer to validate the APIs contributed to the project
                        - Test cases
                        - Will try to contribute for API development 

                        • **DT**
                        - API specs
                        - Reference implementation for some of the APIs
                        - Test cases
                        - Validation of APIs
                        +Topics for Commonality Workstream| • API Spec format
                        • Authentication and Authorization
                        • Should tools for telemetry/scheduling/performance characterizations be based on a technology like Kubernetes?
                        • Use of Intel's OpeNESS platform
                        • Recommended tools for testcases + + + + +## Other Notes +N/A diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d875b80aaa1b2f08fafc56ce2fb9013a0e5da99e --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021/raw.md @@ -0,0 +1,28 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 26-Nov-2021 + +## Attendees +- Jan Friman +- Joachim Dahlgren +- Petar Torre +- Ali Tizghadam +- Felix Dsouza +- Mariusz Sozanski + + +## Goals +- Recap +- Update on API specs +- Q&A + +## Agenda Items + +Item | Description +---- | ---- +Recap | During the last meeting an update of the Quality on Demand APIs have been announced.
                        The API specs have been published last week. Last meeting's presentation slides have been published at https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/documentation/Presentations/QoD-API_Alliance.pdf +Update on API specs | • The updated API specs are now available at https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand
                        • The specs version is now "stable": it won't be altered within the next 2 months to provide a stable basis for initial testing by developers.
                        • All feedback, comments and proposals are welcome! +Q&A | • **Why two similar separate APIs have been created instead of a single one with two features?**
                           We wanted to make things as simple as possible. Although (in fact) currently there is just one common testing API behind, in the future the two QoD may diverge significantly, thus it has been decided to keep them separated. Still, this may be revised later on in further development. + +## Request to participants + • **Any feedback on the current API specs will be appreciated, thank you!**
                        diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..88924d0030df69b5eec50c26270089b3beba9149 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21/raw.md @@ -0,0 +1,28 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-Jan-2022 + +## Attendees +- Petar Torre (Intel) +- Ali Tizghadam (Telus) +- Toshi WAKAYAMA (KDDI) +- Jan Friman (E///) +- Emil Zhang (E///) +- Joachim Dahlgren (E///) +- Christoph Goertz (MobileEdgex) +- Mariusz Sozanski (DT) +- Noel Wirzius (DT) +- Steffen Drüsedow (DT) +- Shilpa Padgaonkar (DT) + +## Goals +Go through last MoM action items +Identify additional tasks, prepare upcoming ones + +Item | Who | Description +---- | ---- | ---- +Open questions from last WG call:
                        • Provide details what would differ in future regarding the 2 APIs
                        • What happens when consumer needs combination of both?
                        •Api to provide the consumer with available profile options | DT | Issue has been updated with answers as latest comments #16 +Issue15
                        •Consider additional specs | E/// |•Emil will prepare the presentation and inform when it needs to be part of hte agenda.
                        •Part of the requirements were presented to the bigger Camara group https://github.com/camaraproject/rep_main/blob/main/WorkingGroups/Commonalities/Camara%20assumptions%20and%20missing%20concepts.pdf. +Issue18
                        •Subactivity to create table to map ‘Throughput_S/M/L’ and ‘LOW_LATENCY’ and standard 3GPP QCI/5QI values. | Telefonica | Doc yet to be created +Split E/// proposals into 3 separate issues:-
                        • GPSI as UE identifier under general label so that wider audience get a say and is not limited to WG members only
                        • Document common terminologies and vocabulary across API families to use issue to be checked with commonalities gruop if it can be addresses by resource description doc and E/// will help in partly contributing to the doc
                        • Authorization related issue should be also under commonalities WG|All | E/// will create the 3 separate issues and add appropriate labels for the same +New issue will be created under QoD WG to explain the impact of possible UE authorization on the current QoD API spec |DT, E/// | E/// will document as comments to this issue how the API would change if checks for authorized UE were to be in scope. https://github.com/camaraproject/rep_main/issues/34 diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..975724f229ffc549b8597028d1b55a78e9da1abd --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04/raw.md @@ -0,0 +1,32 @@ +# Camara QoD meeting +### Date: 04 Feb 2022 + +## Attendees +- **_Ali Tizghadam (Telus)_** +- **_Jose Antonio Ordonez Lucena (TEF)_** +- **_Sylvain Morel (Orange)_** +- **_Toshi WAKAYAMA (KDDI)_** +- **_Jan Friman (E///)_** +- _**Joachim Dahlgren (E///**)_ +- **_Francesc Guim (Intel)_** +- **_Steffen Drüsedow(DT)_** +- **_Shilpa Padgaonkar (DT)_** +- **_Marcin Jarzab (DT)_** + +All QoD minutes link: [https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes](https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes) + +## Goals +- Go through last MoM action items +- Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items +Agenda Item | Who|   +---- | -------- | ---- +Welcome & Recap |  |- Api specs are available at:
                        [https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand](https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand)

                        - Reviews from WG members discussed and worked on using open issues: [https://github.com/camaraproject/rep_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD](https://github.com/camaraproject/rep_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD)

                        - E/// proposals in issue #33 have been split into 4 separate issues (#34 and #36-38):
                           1. Impact of verification for authorised recipient (e.g. UE) on QoD API spec (issue #34)
                           2. GPSI as UE identifier under _general_ label so that wider audience get a say
                           3. Terminology related issue merged with #24 in _commonalities_ group
                           4. Authorisation related issue also under _commonalities

                        - topics started to be addressed within relevant GitHub issues - thanks! +Issue #15
                        Consider additional specs: more network API specifications which have QoS support beyond the well-known NEF APIs| E/// |
                        - E/// is working on new presentation to provide details for extension/changes proposed for issue #15
                        - Proposal to make this a Camara medium-term objective by DT & TEF while waiting for EES/SEAL implementations.
                        - This issue is being marked as QoD-backlog = this is a new label for postponing issues as keeping as backlog +Issue #16
                        Questions on QoD user stories | E///|- new comments (TEF): We should follow user story template discussed in Commonalities WG for every selected use case. Otherwise, some of the details/implications of the user stories are not fully clear.
                        - Issue to be closed and re-opened upon completion of Commonalities User Stories template +Issue #18
                        Subactivity to create table to map ‘Throughput_S/M/L’ and ‘LOW_LATENCY’ and standard 3GPP QCI/5QI values. |Telefónica|- questions 1&2 addressed in December.
                        - Question 3: table mapping activity created as issue #21
                        - to be closed as soon as #21 is developed +Issue #19 & #20 are _enhancements_
                        - Add possibility to specify duration in the QoD APIs
                        - Add new endpoint in QoD API to request available qos_profiles| DT | Issue #19 is under development (DT):
                        - it is not going to be a mandatory feature
                        - An example of B2C "boost activation" use case could be gaming apps (a specific use case may be described in more detail during one of next meetings)
                        - Orange: monitoring of duration and consumption and complementary offer of QoS linked to specific area could be proposed as further enhancement
                        - TEF: this feature will simplify the API consumer life so he does not have to remember to deactivate. But more background functions may be needed for the implementation, therefore implications of what is to be included (e.g. a duration timer) should be analyzed

                        Issue #20 will be labeled as QoD-backlog due to other on-going priorities
                        - the operation is going to be performed through discovery +Issue #21
                        Create a mapping table for qos_profiles |All |Everyone is invited to contribute and add proposed rows to the table. The draft placeholder is located under: [https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/QoSProfile_Mapping_Table.md](https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/QoSProfile_Mapping_Table.md) +Issue #22
                        Document relevant notifications for QoD APIs|All| A placeholder for the list of notifications (e.g. _session_termination_ notification) relevant for the QoD API family has been created: [https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md](https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md)
                        Everyone is invited to contribute to the newly created table. +Issue #34
                        impact of verification for authorised recipient (e.g. UE) on API spec | E/// | issue #36 outcome can impact the QoD API (e.g. GPSI id vs IP identification). Using NEF could be possible to have a translation - to be addressed in #36. diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5f38b28a8d6c11830e75fd1904f05e6c3eea36df --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18/raw.md @@ -0,0 +1,44 @@ +# Camara QoD meeting + +### Date: 18 Feb 2022 + +## Attendees + +* *Petar Torre (Intel)* +* *Thomas Vits (TangibleXR)* +* *Jose Antonio Ordonez Lucena (TEF)* +* *Toshi WAKAYAMA (KDDI)* +* *Jan Friman (E///)* +* *Emil Zhang (E///)* +* *Christoph Goertz (MobileEdgex)* +* *Marcin Jarzab (DT)* + +All QoD minutes link: [https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes](https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes) + +## Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| Welcome & Recap | | \- New API version 1\.2\.0 specs are available at:
                        [https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand](https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand)
                        \- Reviews from WG members discussed and worked on using open issues: [https://github.com/camaraproject/rep\_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD](https://github.com/camaraproject/rep\_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD)
                        \- topics started to be addressed within relevant GitHub issues \- thanks\! | +| | | | +| *CLOSED ISSUES* | | | +| Issue #19: **closed**
                        \- Add possibility to specify duration in the QoD APIs | DT | [Issue #19](https://github.com/camaraproject/rep\_main/issues/19) has been addressed:
                        \- version 1\.2\.0 of the API definitions uploaded to *QualityOnDemand* subdirectory.
                        The new version implements the duration parameter of *CreateSession* component schema and a *SESSION\_TERMINATED* event when the session ends/expires.
                        \- The duration property is not going to be a mandatory parameter and is defined as follows:
                        *`(...)`*
                        `duration:`
                        ` type: integer`
                        ` example: 86400`
                        ` description: `
                        `____Session duration in seconds. Maximal value of 24 hours is used if not set.`
                        `____After session has expired the client will receive SESSION_TERMINATED event. See`
                        `____notification callback.`
                        ` format: int32`
                        ` minimum: 1`
                        ` maximum: 86400`
                        *`(...)`* | +| Issue #16 **closed**
                        Questions on QoD user stories | E/// | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.
                        \- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template | +| Issue #18 **closed**
                        Subactivity to create table to map ‘Throughput\_S/M/L’ and ‘LOW\_LATENCY’ and standard 3GPP QCI/5QI values. | Telefónica | \- questions 1&2 addressed in December\.
                        \- Question 3: table mapping activity created as issue \#21 in order to close this issue\. | +| | | | +| *CURRENT ISSUES* | | | +| Issue #21
                        Create a mapping table for qos\_profiles | TEF/DT? | The draft placeholder is located under: [https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/QoSProfile\_Mapping\_Table.md)
                        \* DT: There are multiple values of QCI/5QI to be mapped: configuration blueprint to be done by API vendor
                        \* TangibleXR: a possible workaround is API Discovery; the parameter options would be explained in API and translated into proper values. Defining normative values may not be in scope of Camara (but rather reserved for each business/CSP on their own)
                        \* TEF: then a problem arises with consistency and providing quality of UX. There are plenty of options, but to ensure consistent testing, we need a ref. value from each tag.
                        \* We agree to create an initial blueprint draft, possibly created by TEF (and DT co-operation) to put this discussion further and see if we can create a commonly accepted document | +| Issue #22
                        Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created: [https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/Notifications.md](https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/Notifications.md)
                        \* currently only *session\_termination* notification is present
                        \* please document which other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue #15
                        Consider additional specs: more network API specifications which have QoS support beyond the well-known NEF APIs | E/// | \* to be closed following contribution by E/// to Camara - being investigated by Commonalities group
                        \* update coming in GitHub next week before the Camara Commonalities group meeting so it can be discussed then | +| Issue #20: *enhancement*
                        \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #20 will be labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery | +| Issue #34
                        impact of verification for authorised recipient (e.g. UE) on API spec | E/// | issue #36 outcome can impact the QoD API (e.g. GPSI id vs IP identification). Using NEF could be possible to have a translation - to be addressed in #36. | +| | | | +| AOB | | | +| | | 1\. Next QoD meeting in two weeks on the 4th of March\.
                        2\. OPAG GSMA is interested in collaboration\, a\.o\. in QoD specification\. | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..142abe6f30e31e15b78b19aa6722b54a9998cbae --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04/raw.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 4 Mar 2022 + +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Attendees + +* **Jose Antonio Ordonez Lucena (TEF)** +* **Petar Torre (Intel)** +* **Ali Tizghadam (Telus)** +* **Andrew Wajs (Scenera)** +* **Sylvain Morel (Orange)** +* **Toshi WAKAYAMA (KDDI)** +* **Jan Friman (E///)** +* **Emil Zhang (E///)** +* **Joachim Dahlgren (E///)** +* **Shilpa Padgaonkar (DT)** +* **Slawomir Tkacz (DT)** + + +### Goals + +* Go through issues/action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Camara announced at MWC 2022.
                        **NEW** repository structure:
                        \* the steering committee decided to move the working groups and QoD API subproject to separate repositories
                        \* new QoD repo address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        \* new organisation of directories | +| | | \- API version 1\.2\.0 \(see also new Commonalities [issue #25](https://github.com/camaraproject/WorkingGroups/issues/25)) specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue #21 -> QoD#1
                        Create a mapping table for qos\_profiles | TEF/DT/
                        /All? | The draft placeholder has been relocated to:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                        \* Multiple values of QCI/5QI to be mapped, possibly via a configuration blueprint

                        \* TEF: 5QI initial investigation by TEF leads to suggest to limit the throughput to two values: standard and premium for validation purposes. At least as internal reference validation for Camara.
                        \* standard NEST for eMBB slice -> 3GPP 5QI: 1,2,5,6,7,8,9

                        \* Orange: Maybe a range of values possible for operators to choose could be possible.
                        \* DT: could we leave this to operators, so they can customize their offering (as, e.g., cloud operators do).
                        \* Intel: we need to guarantee consistency towards developers by offering at least similar values.

                        \* TODO actions:
                        \- please reflect your proposals/comments under [GitHub issue #1](https://github.com/camaraproject/QualityOnDemand/issues/1)
                        \- check internally with teams what has been tested/proposed | +| Issue #22 -> QoD#2
                        Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                        \* currently only *session\_termination* notification is present

                        \* E///: add QoS monitoring event notifications from NEF - it may be a candidate for future notification
                        \* DT: we were not able to validate other notifications internally until now
                        \* Orange: specific feedback on QoS event, tested in Orange, to be discussed internally if other notifications are relevant

                        \* TODO: please document through the [GitHub issue](https://github.com/camaraproject/QualityOnDemand/issues/2) if other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue #15 -> #6
                        Consider more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                        \* consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog. | +| Issue #20 -> #7
                        \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) will be labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery | +| Issue #34 -> #8
                        impact of verification for authorised recipient (e.g. UE) on API spec | E/// | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC. | +| Issue #16 / #3 *closed*
                        Update of QoD user stories | E/// | \- We should follow user story template discussed in Commonalities WG for every selected use case\.
                        \- Issue has been closed \- QoD user stories will be updated upon completion of Commonalities User Stories template\. | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 18th of March\. | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..51cbb4790c2e91d05b91a9ae5c6aaceffaeefda8 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18/raw.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 18 Mar 2022 + +## Attendees + +* **Petar Torre (Intel)** +* **Cesc Guim (Intel)** +* **Toshi WAKAYAMA (KDDI)** +* **Jan Friman (E///)** +* **Emil Zhang (E///)** +* **Joachim Dahlgren (E///)** +* **Eric Murray (Vodafone)** +* **Kevin Smith (Vodafone)** +* **Ivan Nieto (Vodafone)** +* **Steffen Drüsedow (DT)** +* **Marcin Jarząb (DT)** + +
                        +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | **NEW** repository structure:
                        \* the steering committee decided to move the working groups and QOD API subproject to separate repositories
                        \* new QoD repo address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        \* new organisation of directories | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue QoD#1
                        Create a mapping table for qos\_profiles | TEF/DT? | A reference draft has for discussion been published to:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                        \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                        \* ToDO: please verify and comment through the GITHUB ISSUE your position on such mapping
                        \* change L to "up to unlimited" proposal as in Vodafone e.g. | +| Issue QoD#2
                        Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                        \* currently only *session\_termination* notification is present
                        \* ToDo: please document through issue if other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue QoD#3 Questions on QoD user stories | DT | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.\- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template next week \(TODO\) | +| Issue #6
                        Consider additional specs: more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                        consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog.
                        \* ToDo: to be closed as the UEid has been proposed. | +| Issue #7
                        \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) will be labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery | +| Issue #8
                        impact of verification for authorised recipient (e.g. UE) on API spec | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                        \* todo: please comment in the issue
                        \* the auth by GPSI is initially accepted by the workgroup - still, the impact on API def is to be analyzed | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 1st of April\. | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b2704b4b0b55a333c31fc8c4d879b8448ce6030f --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01/raw.md @@ -0,0 +1,56 @@ +# Camara QoD meeting + +### Date: 1st of April 2022 + +## Attendees + +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** +* ***Tomas Vits (MobiledgeX)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** + +
                        + +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue QoD#1
                        Create a mapping table for qos\_profiles | TEF/DT | A reference draft has for discussion been published to:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                        \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                        \* change L to "up to unlimited" or rather "best effort" (Vodafone proposal), see [GitHub comment](https://github.com/camaraproject/QualityOnDemand/issues/1)
                        \* DT agrees with Vodafone comments and notes that it this mapping table is just an example that could be used for validations within the alliance. 
                        \* Orange: Maintaining a separate YAML for every new profile is not manageable and this could instead be delegated to the discovery service as specified in issue #7
                        \* DT:  The discovery API is in our backlog and once implemented, the separate YAML constructs wont be needed anymore.
                        \* ToDO: please verify and comment through the GitHub ISSUE your position on such mapping | +| Issue QoD#2
                        Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                        \* currently only *session\_termination* notification is present | +| Issue QoD#9
                        security requirements bug | DT | \* corrected security requirements mistake/"typo" (referring to *APIKeys* instead of *oAuth2ClientCredentials*) with PR#10
                        \* Orange is working on a possible real-life implementation. Lab with E/// SCEF, checking both radio access types.
                        \* DT: working as well on NEF.
                        -> We could validate it in both cases, hoping to validate it additionally with a NEF emulator.
                        \* Intel prepared a NEF emulator, investigating internally on its capabilities ([Commonalities issue #26](https://github.com/camaraproject/WorkingGroups/issues/26)). | +| NEW TOPIC | Orange | \* Orange Q: If an API such as the one used for QoD could be applied for both 4G/5G, what should be the validation process? 
                        DT-> This question  could be valid for more than just the QoD API and a new issue in commonalities will be created to discuss the details.
                        ToDo: create issue in  commonalities issue for verification of API 4G/5G capabilities

                        Orange: We wish to provide reference implementation of QoD APIs and validate it against SCEF. Would be interested in alignment with other partners on this. 
                        DT: working on implementation as well and will validate against NEF. Another validation will be mostly don't against NEF emulator contributed to community (possibly from Intel) | +| | | | +| *QOD-BACKLOG* | | | +| Issue QoD#3 Questions on QoD user stories | DT | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.
                        \- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template next week
                        ToDo:
                        \* Open new issue to contribute user stories based on template
                        \* Open another issue to contribute api documentation based on template | +| Issue #6
                        Consider additional specs: more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                        consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog.
                        \* DT: related to GPSI GH issue on Commonalities
                        \* E/// closed this issue, please see related [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4) for further comments and discussion. | +| Issue #7
                        \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1)) | +| Issue #8
                        impact of verification for authorised recipient (e.g. UE) on API spec | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx)   to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                        * the auth by GPSI is initially accepted by the workgroup - still, the impact on API def is to be analyzed
                        * thank you for comments in the issue | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 22nd of April\. | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e17ebd74340115e0004246ead9941d1d14f5fdb3 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22/raw.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +### Date: 22nd of April 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** + +
                        +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 6 , Closed: 5 ]** | +| Issue QoD#1
                        *Create a mapping table for qos\_profiles* | TEF/DT | A reference draft has for discussion been published to:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                        \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                        \* change L to "up to unlimited" or rather "best effort" (Vodafone proposal), see [GitHub comment](https://github.com/camaraproject/QualityOnDemand/issues/1)
                        \* DT agrees with Vodafone comments and notes that it this mapping table is just an example that could be used for validations within the alliance. 
                        \* Orange: Maintaining a separate YAML for every new profile is not manageable and this could instead be delegated to the discovery service as specified in issue #7
                        \* DT:  The discovery API is in our backlog and once implemented, the separate YAML constructs wont be needed anymore.
                        \* ToDO: please verify and comment through the GitHub ISSUE your position on such mapping
                        **Status : Open/Active discussion**  
                        **Proposed action: Close** | +| Issue QoD#2
                        *Document relevant notifications for QoD APIs* | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                        [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                        \* currently only *session\_termination* notification is present
                        **Status : Open/Active**
                        **Proposed action : Closed (Comment: Issue closed with Living document only)** | +| Issue QoD#12
                        *Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template
                        \* *DT is working internally (DOC internal review)*
                        **Status : Open/Active** | +| **NEW Topic** | | | +| Issue #11
                        *\- Is enum the best choice for qos\_profile* | Orange | -What if a client needs a QoS profile with LOW\_LATENCY and THROUGHPUT\_L?
                        -We would need to add an enum key that represents this combination and also a new key for all other relevant ones.
                        -We could associate each profile with values based on the power of two (1, 2, 4, 8, 16...) and compose them via an OR operation. 
                        *DT comment:*
                        -CAMARA goal is to define some general approach -> production deployments will differ 
                        -Discovery profile API might be solution to get list of QOS Profile "flavours"
                        -Simmilar approach applied by Public cloud vendors (Instance flavours for many use-cases)
                        -Will depend on Operator and Technology (e.g. GSMA based blueprint possible)
                        **Status: Open/Discussion started**
                        **Proposed action: Close (?) or just propose more details regarding the requirement** | +| **QoD Backlog** | | | +| Issue #7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))
                        \* DT will check internaly with DEV team | +| Issue #8
                        *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4):
                        the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                        \* the auth by GPSI is initially accepted by the workgroup - still, **the impact on API def is to be analyzed**
                        \* technical discussion on-going (include Commonalities) : Security and Auth will not be part of API
                        \* E/// proposed to close
                        **Status: Open/Active discussion**
                        **Proposed action: Continue effort (define user stories and design)** 
                           **->Organize global meeting to discuss within broader audience (@M.K)** | +| **AOB** | | | +| | | 1\. GSMA OPG/OPAG expressed interest in collaboration with CAMARA project
                          \* *QoS/NW Events/Mobility and others are on PRIO list (SBI-NR 3GPP API list) : CAMARA alligment is being discussed* 
                          \* EDGE API contribution diccussed      
                        2\. Next QoD meeting in two weeks on the 6th of May\.
                        3\. Patrice@Orange \- Notifications / Authentications on server side
                          -> Have owners of security topic and prepare dedicated technical meeting (related to #8) | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2a5b170044f785baa52651f89a4ea30089e5fcbf --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06/raw.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +### Date: 6-th of May 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** + +
                        +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 3 , Closed: 8 ]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template
                        \* *DT is working internally (DOC internal review)*
                        **Status : Open/Active development \* Update : User stories and API-docs under internal review in DT** | +| Issue #7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))
                        **Status : Open/Active development**
                        \* DT will check internaly with DEV team -> **agreed and defined within "current" Sprint scope**
                        **\* Activity started and "internal" proposal being discussed : *(on-going activity)*** | +| **NEW ISSUES** | | | +| *Issue not assigned ID*
                        -Notifications / Authentications on server side | Orange | Patrice@Orange - Notifications / Authentications on server side
                         \* Have owners of security topic and prepare dedicated technical meeting (related to #8)
                         \* *Topic to be discussed within Commonalities group (TBC)* | +| Testing and Validation | DT,
                        Orange | \* we need to start to summary leassons learnt from Dev/Validate   
                        \* pririties on validation , make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT internal solution TBC  
                          -> what is the requirement / QoS profiles : on-demand resource reservation and numbers 
                            UPlink flow for Video/Control function 
                            based on the solution definition of testing requirments would be easier to define and understand 
                        \* Orange 
                          conditions in which API is called etc
                           ->  will prepare some short material  | +| Transform Function | TEF | Goal : Service API will deliver consistent funcionality for End-users
                        \- Metrics names and target goals 
                        \- How to include into Transform Function 
                        \- testing workflow defined and included: CAMARA API / Transform / NEF 
                        -> short overview of idea be prepared by TEF | +| **QoD Backlog** | | | +| Issue #8
                        *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4):
                        the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                        \* the auth by GPSI is initially accepted by the workgroup - still, **the impact on API def is to be analyzed**
                        \* technical discussion on-going (include Commonalities) : Security and Auth will not be part of API
                        \* E/// proposed to close *(Confirmed during the meeting)*
                        **Status: Open/Active discussion -> Close (@Eric)** | +| **AOB** | | | +| | | 1\. Organization of QoD community \(R&D improvements\)
                          \* GSMA OPAG/OPG collaboration / contribution still being discussed       
                        2\. Next QoD meeting in two weeks on the 20th of May\. | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fa0086d808d3c63c047f58a2ca58ae890dbc4b3d --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20/raw.md @@ -0,0 +1,44 @@ +# Camara QoD meeting + +### Date: 20th of May 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** + +
                        +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 2 , Closed: 9 ]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template

                        **Status : Open/Active development *(under-review)***   
                         **- UPDATE : User story and Latency/Bandwidth API-docs under internal review** | +| Issue #7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                        **Status : On-Hold**
                        **\* Activity started and "internal" proposal being discussed**
                         **\- UPDATE : Discussed use cases \(e\.g\. Network Slice\) include feedback from Hyprescalers \- under consideration** | +| **NEW ISSUES** | | | +| Testing and Validation | DT,
                        Orange | \* We need to start to summary leassons learnt from Dev/Validate   
                        \* Priorities on validation, make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT internal solution (**TBC**)  
                           - QoS profiles: what is the requirement  
                           - On-demand resource reservation and numbers for UL/DL flows
                           - Testing requirements would be easier to define and understand 
                           - Example: Video/Control function based on the solution definition. 
                           **UPDATE (DT/BMW/Valeo AVP):** 
                            [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                            - The data packets are transferred with always the same delay even under high load conditions (stable low latency) or           the bandwidth is kept on the same level even under high load (stable bandwidth).
                            - During the time of the car maneuvering the data connection is prioritized against other data connections in the same         mobile cell.
                            
                        *\* Example sequence diagram is requested with call flows    (Terminal -> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction )*     SeNF - Service Enabling Network Function 
                        ***\* Sample application to be considered***
                            
                        \* Orange : conditions in which API is called
                           -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                        \* Metrics names and target goals 
                        \* How to include into Transform Function 
                        \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                        **Transform Function**       
                        \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                        *\- Focus on 3GPP *& CAMARA* API with Mappping Table presented (PPT will be distributed)* | +| **QoD & API Backlogs** | | | +| Issue #8
                        *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                        This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4)
                        **Status: Closed** | +| API Backlog : 

                        Issue #29
                        - API to Request the Status of the Network Traffic   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                        When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 
                        \* Trade off between video quality and delay. If the delay reaches a threshold it is more desirable to reduce video quality than to have the highest possible video quality. It is desirable to reduce the video quality if it reduces the network delay for the video delivery.
                        \* Monitor API which provides an indication of the status of the network (delay and traffic levels and other parameters that would indicate the performance of the network).
                        \* Based on the status,the Application adjusts the encoding level to best suite the condition in network. 

                        **Status: Open / Discussed** 
                        \* QoD related topic are discussed 
                         - Monitor API and Manage the "parameters" 
                         - QoD members are encouraged to partcipate in the discussion
                         - Let's discuss on the next meeting | +| **AOB** | | | +| | | 1\. GSMA OPG/OPAG Meetings \[24\-25\.05\] 
                          \* Encouraged F2F Internal meetings to discuss issues & ideas        
                        2\. Next QoD meeting in two weeks on the 3rd of June | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d77ab929202ef94c162604e3b3ef0bc5c43816b7 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03/raw.md @@ -0,0 +1,43 @@ +# Camara QoD meeting + +### Date: 3rd of June 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** +* ***Tuan Tran (Broadpeak)*** +* ***Assane Niang (Orange)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 2 , Closed: 9 ]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template

                        Status : Open/Active DEV *(Under-review /* **No-Change )** | +| Issue QoD#7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                        **Status : On-Hold (No-Change)** | +| **NEW ISSUES / Discuss point** | | | +| Testing and Validation | DT,
                        Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                        \* Priorities on validation, make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT solution developed with partners: AVP sample application presented
                            [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                         *\- Following components discussed based on the AVP        Terminal \-> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                             \* SeNF - Service Enabling Network Function 
                           AVP Use case with Camara QoD description:
                           [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                           
                           -> M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)

                        \* Orange : conditions in which API is called
                         -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                        \* Metrics names and target goals 
                        \* How to include into Transform Function 
                        \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                        **Transform Function**       
                        \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                        *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                        - **On-going action proposed : How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management** 
                         **-> Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **QoD & API Backlogs** | | | +| API Backlog : 

                        Issue #29
                        - API to Request the Status of the Network Traffic   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                        When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 
                        \* Trade off between video quality and delay. If the delay reaches a threshold it is more desirable to reduce video quality than to have the highest possible video quality. It is desirable to reduce the video quality if it reduces the network delay for the video delivery.
                        \* Monitor API which provides an indication of the status of the network (delay and traffic levels and other parameters that would indicate the performance of the network).
                        \* Based on the status,the Application adjusts the encoding level to best suite the condition in network. 
                        [https://github.com/camaraproject/WorkingGroups/issues/29](https://github.com/camaraproject/WorkingGroups/issues/29)

                        **Status: Open / Discussed** 
                        \* QoD related topic are discussed 
                         - Monitor API and Manage the "parameters" 
                         - QoD members are encouraged to partcipate in the discussion
                         
                        **-> Andrew will preapre material to be presented on the API Backlog** | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 17th of June | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8a267b6b6f81b8139c540c77a4b0af6c11c71c7a --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17/raw.md @@ -0,0 +1,52 @@ +# Camara QoD meeting + +### Date: 17 of June 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Jose Antonio Ordonez (TEF)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** +* ***Eric Muray (Vodafone)*** +* ***Tuan Tran (Broadpeak)*** +* ***Assane Niang (Orange)*** +* ***MBENGUE Assane Niang (INNOV/NET)*** +* ***Serena (SKT)*** +* ***Thorsten Lohmar*** +* ***Milan Lalovic (BT)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \- Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 12 [ Open: 3 , Closed: 9 ]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template

                        Status : Open/Active DEV *(Under-review /* **No-Change )** | +| Issue QoD#7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \- the operation is going to be performed through discovery
                        \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                        **Status : On-Hold (No-Change)** | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                        Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                        \* Priorities on validation, make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT solution developed with partners: AVP sample application presented
                            [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                        *\* Following components discussed based on the AVP*
                         *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                           (SeNF - Service Enabling Network Function)
                         - AVP Use case with Camara QoD description
                           [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                           **Update [3/6]:**
                            M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)

                        \* Orange : conditions in which API is called
                         -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                        \* How to include into Transform Function 
                        \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                        **Transform Function**       
                        \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                        *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                        - On-going action proposed :    How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                        **UPDATE: Based on agreement during the community meeting [3/6], SeNF should contain Transform Function** | +| Issue#13 -  *Flow Description Mapping* | Ericsson | **Goal : Enhance QoD API with "Flow Description" already defined in 3GPP NEF**
                        \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                        \* Lose the flexibility to define multiple flows in an AS session. 
                        *\* Presented on the meeting and will improve based on community feedback*

                        **DECISION: Continue with User-Story and next vote via commnunity if include into the API release.** | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : 

                        Issue #29
                        *-* *API to Request the Status of the Network Traffic*   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                        When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera.
                        The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 

                        **Status: Open/Discussed** **within API-Backlog**
                        **\- UPDATE: Use\-case proposal presented on the API Backlog meeting** | +| Issue #30
                        - *API to Route Traffic to a Specific Slice on the Network* | | **Use Case: Selectively Routing Traffic to a Network Slice**
                        An application has video traffic and configuration traffic. The application routes its Configuration Traffic over a slice
                        with higher quality of service and routes the video traffic over a slice with a lower quality of servi

                        **Status: Open/Dicussed within the API-backlog : might be related to QoD** | +| QoD Enhancement 
                        - *QoS Session reservation time extend* | Microsoft | **Goal: API enhancement to enable on-going QoS session renewal**
                        \* Currently QoD session can be specified with session duration \*Enhancement proposed : API for application extend/renew of on-going session (leasing a resource for a limited time and renewing the lease before it lapses until it is no longer needed) | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 3rf of July
                        2\. Please contact topic owner \(@DT\) with any issues or requests | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c7cfd73539ed33766fd739b7436832c220e8e349 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01/raw.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 1st of July 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Eric Muray (Vodafone)*** +* ***Serena (SKT)*** +* ***Milan Lalovic (BT)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \* API version 1.2.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                        \* Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 12 [ Open: 3 , Closed: 9 ]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | \* As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template

                        Status : Open/Active DEV *(Under-internal review)* | +| Issue QoD#7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                        \* the operation is going to be performed through discovery
                        \* could be an additional way of addressing issue #1 (see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                        **Status : On-Hold (No-Change)** | +| Issue QoD#13
                        - *"Flow Description" Mapping* | Ericsson | Issue #13 : Enhance QoD API with "Flow Description" already defined in 3GPP NEF
                        \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                        \* Lose the flexibility to define multiple flows in an AS session. 
                        \* Proposal introduces API to define IP-Flows for single QoS session and assigned Profile
                        *\* Presented on the meeting and will improve based on community feedback*

                        **DECISION: Continue with User-Story and next community voting if include into the API release. UPDATE [1.07]: DT discussed proposal internaly, comments and communication on-going**  | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                        Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                        \* Priorities on validation, make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT solution developed with partners: AVP sample application presented
                            [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                        *\* **Following components discussed based on the AVP***
                         *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                           (SeNF - Service Enabling Network Function)
                         - AVP Use case with Camara QoD description
                           [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                        **Update [3.06]:** M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)
                        \* Orange : conditions in which API is called
                         -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **GOAL : Service API will deliver consistent funcionality for End-users**
                        \* How to include into Transform Function 
                        \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                        **Transform Function**       
                        \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                        *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                        - On-going action proposed : How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                        **UPDATE [3.06]: Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **API Improvements / Updates** | | | +| QoD API Update 
                        *(error codes / description)* | DT | **QoD API - Please verify and update QoD def to v. 1.2.1 #14 :** [https://github.com/camaraproject/QualityOnDemand/pull/14](https://github.com/camaraproject/QualityOnDemand/pull/14)
                        \* No change in API functionality \* Error codes modified (improved description) and new added \* API description change  | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : *Issue* *#29*
                        *-* *API to Request the Status of the Network Traffic*   | Scenera | **Use Case: Adapting Video Encoding to the Network Conditions**
                        When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 

                        **Status: Open/Discussed** **within API-Backlog** 
                        Decision (TBC) : Still not decided where to assign | +| API Backlog : *Issue #30* 
                        - *API to Route Traffic to a Specific Slice on the Network* | Scenera | **Use Case: Selectively Routing Traffic to a Network Slice**
                        An application has video traffic and configuration traffic.
                        The application routes its Configuration Traffic over a slice with higher quality of service and routes the video traffic over a slice with a lower quality of service

                        **Status:** **CLOSED@API-Backlog** : [https://github.com/camaraproject/WorkingGroups/issues/30](https://github.com/camaraproject/WorkingGroups/issues/30)
                        Update [1.07] - Continue with Use case description to fit QoD requirements.  - Material presented / improvements requested (mobile connectivity / IP-Flows) | +| QoD Enhancement 
                        - *QoS Session reservation time extend* | Microsoft | **Goal: API enhancement to enable on-going QoS session renewal**
                        \* Currently QoD session can be specified with session duration \* Enhancement proposed : API for application extend/renew of on-going session (leasing a resource for a limited time and renewing the lease before it lapses until it is no longer needed)

                        **UPDATE (1.07) : Request for Microsoft confirmation**  - Ownership (proposal, user story etc.) and community final agreement (TBA) | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the July 15/2022
                        2\. Please contact topic owner \(marcin\.jarzab@external\.telekom\.de\) with requests/issues | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ad12d7cf7cc3e2ce7fd7ebde971480ec3511431b --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15/raw.md @@ -0,0 +1,47 @@ +# Camara QoD meeting + +### Date: 15th of July 2022 + +## Attendees + +* Marcin Jarząb (DT) +* Steffen Drüsedow(DT) +* Toshi WAKAYAMA (KDDI) +* Petar Torre (Intel) +* Tuan Tran (Samsung) +* Milan Lalovic (BT) +* Mike Bowring (Spry fox networks) +* Ramesh Shanmugasundaram (Spry fox networks) +* Ivan Nieto (Vodafone) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| **CURRENT STATUS** | | | +| *Overview* | | \* Currently contributed API definition needs to be updated for eg. to incorporate the versioning concept agreed within commonalities. Please see newly created issue [https://github.com/camaraproject/QualityOnDemand/issues/20](https://github.com/camaraproject/QualityOnDemand/issues/20)

                        \* Reviews from WG members discussed and worked on using open issues:
                        [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        \- topics started to be addressed within relevant GitHub issues | +| *Highlights* | | \* API documentation is contributed, waiting on review by the group (TBA)
                        \* API code will be contributed until end of July by DT and first complete version 0.x of the API will be on GitHub | +| **CURRENT ISSUES** | | **Total:14 [Open:3, Closed:11]** | +| Issue QoD#12
                        *\- Create user stories for QoD in line with Commonalities standard* | DT | \* As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized 
                          to align the QoD User Stories with the Camara common template.
                        \* Contribute user stories based on template.

                        Update (15.07) Status : Closed / In-review with following pull-requests 
                        \* User Story DOC - [https://github.com/camaraproject/QualityOnDemand/pull/19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                        \* Latency API - [https://github.com/camaraproject/QualityOnDemand/pull/18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                        \* BW API - [https://github.com/camaraproject/QualityOnDemand/pull/17](https://github.com/camaraproject/QualityOnDemand/pull/17) 

                        **Reviewer: *Support from Intel on reviewing the PR's.***

                        **Comment:**
                        -> Glossary DOC in commonalities (in-review) applicable to introduce&define common vocabulary (e.g. App-Flow/UL/DL) 
                        [https://github.com/camaraproject/WorkingGroups/pull/52](https://github.com/camaraproject/WorkingGroups/pull/52) | +| Issue QoD#7
                        *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | **Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities**
                        \* the operation is going to be performed through discovery,
                        \* could be an additional way of addressing issue #1 (see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1)).

                        **Status : On-Hold** | +| Issue QoD#13
                        - *"Flow Description" Mapping* | Ericsson | **Issue #13: Enhance QoD API with "Flow Description" already defined in 3GPP NEF**
                        \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                        \* Lose the flexibility to define multiple flows in an AS session, 
                        \* Proposal introduces API to define IP-Flows for single QoS session and assigned Profile,
                        *\* Presented on the meeting and will improve based on community feedback.*
                        **UPDATE [15.07]: DT discussed proposal internaly and review provided.** | +| Issue QoD#20
                        *- Reset QoD API version* | DT | **Issue #20:** **Reset QoD API version**\* Versioning related guidelines agreed within commonalities working group, the QoD API version needs to be reset (e.g 0.x) | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                        Orange | **GOAL: We need to start to summarize lessons learnt from Dev/Validation**   
                        \* Priorities on validation, make some progress 
                          -> test cases definition for BW/Latency management  
                        \* DT developed PoC with partners: AVP sample application presented
                            [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                        *\* **Following components discussed based on the AVP***
                         *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                           (SeNF - Service Enabling Network Function)
                         - AVP Use case with Camara QoD description
                           [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                        **Update [3.06]:**
                        \* M.Jarzab & Morell will colaborate on further enhancements (UML, Call-flow / considering access technology 4G/5G NSA/SA)
                        \* Orange : conditions in which API is called
                         -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **GOAL : Service API will deliver consistent funcionality for End-users**
                        \* How to include into Transform Function 
                        \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                        **Transform Function**       
                        \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                         *\- Focus on 3GPP & CAMARA*
                        *\** API with Mappping Table presented (PPT will be distributed)
                         - On-going action proposed: How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                        **UPDATE [3.06]: Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **API Improvements / Updates** | | | +| QoD API Update 
                        *(error codes / description)* | DT | **QoD API - Please verify and update QoD def to v.1.2.1 #14 :** [https://github.com/camaraproject/QualityOnDemand/pull/14](https://github.com/camaraproject/QualityOnDemand/pull/14)
                        \* No change in API functionality, 
                        \* Error codes modified (improved description) and new added, 
                        \* API description change.  
                         -> **UPDATE [15.07]** "Reverted" due to decision to change API versioning to 0.x since backward compatibility still not supported | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : *Issue #30* 
                        - *API to Route Traffic to a Specific Slice on the Network* | Scenera | **Use Case: Selectively Routing Traffic to a Network Slice**
                        An application has video traffic and configuration traffic.
                        The application routes its Configuration Traffic over a slice with higher quality of service and routes the video traffic over a slice with a lower quality of service.

                        **Status:** **CLOSED@API-Backlog** : [https://github.com/camaraproject/WorkingGroups/issues/30](https://github.com/camaraproject/WorkingGroups/issues/30)
                        **Update [1.07]** \* Continue with Use case description to fit QoD requirements, 
                        \* Material presented / improvements requested (mobile connectivity / IP-Flows). | +| Enhancement :
                         QoS Profiles Map | BT | \* Discuss idea from BT to enhance current QoS profiles mapping table to better fit actual mappings with Network Capabilities, 
                        \* Consider Transform Function as “component” which is responsible for those mappings, 
                        \* Update current QoD profiles (Low\_Latency, S\_Throughput, … -> High Priority Queue ), 
                        \* Issue will be created with details and proposed approach.  

                        [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/BT\_Contributions\_CAMARA\_QoD.pdf](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/BT_Contributions_CAMARA_QoD.pdf)
                        | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the July 29/2022
                        2\. Please contact topic owner \(marcin\.jarzab@external\.telekom\.de\) with requests/issues | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17213d2b23f3d7dc888274bae415453a616bef87 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29/raw.md @@ -0,0 +1,47 @@ +# Camara QoD meeting + +### Date: 29th of July 2022 + +## Attendees + +* Toshi Wakayama (KDDI) +* Animesh Attri (Telus) +* Emil Zhang (Ericsson) +* Kevin (Vodafone) +* Kevin Zu (Verizon) +* José A. Ordóñez Lucena (Telefonica) +* Morel Sylvain (Orange) +* Mbengue Assan Niang (Orange) +* Tuan Tran (Broadpeak) +* Ramesh Shanmugasundaram (Spry fox networks) +* Herbert Damker (DT) +* Anja Gerlach (DT) +* Shilpa Padgaonkar (DT) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | | +| Issues and Pull Requests | |
                        • Issues:19 [Open:8, Closed:11]
                        • Pull requests:11 [Open:7, Closed: 4]
                        | | +| **HIGHLIGHTS** | |
                        • QoD service implementation contributed to Camara
                        • QoD API version reset done to 0.1.0 
                        | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        Status: Ongoing | Ericsson |
                        • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                        • Herbert will create the new issues as agreed
                        | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                        *Status: New* | DT |
                        • API version has been reset to 0.1.0. 
                        • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                        • Agreed reviewers
                          • Jose
                        • Request additional members to nominate themselves as reviewers 
                        | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution 
                        *Status: New* | DT |
                        • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                        • No reviweres selected in today's meeting
                        • Details of the contribution are available here 
                        • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD)
                          [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                        | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                        *Status: New* | DT |
                        • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                        • New topics from Sylvain and Jose:
                          • How to ensure completeness of security review? Issue to be opened in commanalities by Shilpa
                          • In what format should test cases be contributed? Issue to be opened in Commonalities by Shilpa
                          • Can DT provide some sample test data for QoD tests? DT will check internally and get back on this topic
                        | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                        Status: Ongoing | DT
                        Intel
                        Vodafone | Following pull requests are currently in review
                        • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                        • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                        • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                        Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        Status: New | |
                        • Will be fixed with a PR
                        | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                        Status: New | Verizon |
                        • Points 1,2,3 are either covered as a part of ongoing Documentation reviews or are a duplicate of [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        • Point4 is already in the internal backlog of DT for one of the upcoming releases.
                          Shilpa will create an issue in QoD to address this point..
                        | | +|
                        **NEW ISSUES / Discussion point** | | | | +| | |
                        • Herbert: Is approval from 2 reviewers enough to merge a PR?
                        • Shilpa: How long should an inactive review stay open?
                        • Jose: The current implementation does not include in scope the consent mangement aspect. Shilpa will restart this discussion in Commanalities as it has impact on several other API families.
                        | | +| **AOB** | | | | +| | | Next QoD meeting in two weeks on the Aug 12/2022 | | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ea3ca806726007a6cb6417f3a61d3dba316b4447 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12/raw.md @@ -0,0 +1,52 @@ +# Camara QoD meeting + +### Date: 12th August 2022 + +## Attendees + +* Toshi Wakayama (KDDI) +* Emil Zhang (Ericsson) +* Jan Friman (Ericsson) +* Eric Murray (Vodafone) +* Andrew Wajs (Scinera) +* Syed R (Verizon) +* Patrice Conil (Orange) +* Animesh Attri (Telus) +* Shilpa Padgaonkar (DT) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | | +| Issues and Pull Requests | |
                        • Issues:26[Open:14, Closed:12]
                        • Pull requests:12 [Open:8, Closed: 4]
                        | | +| **HIGHLIGHTS** | |
                        • Patrice would like to contribute a second reference implementation for QoD. To be checked with Markus Kümmerle where we can place this
                        | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        Status: Ongoing | Ericsson |
                        • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                        • Shilpa will create the new issues as agreed
                        • This later comments will be reviewed by Eric to see if this issue can be closed.
                        | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                        *Status: New* | DT |
                        • API version has been reset to 0.1.0. 
                        • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                        • Agreed reviewers
                          • Jose and Emil
                        | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution 
                        *Status: New* | DT |
                        • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                        • No reviweres selected in today's meeting
                        • Details of the contribution are available here 
                        • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD) [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                        | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                        *Status: New* | DT |
                        • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                        • No reviewers yet
                        | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                        Status: Ongoing | DT
                        Intel
                        Vodafone | Following pull requests are currently in review
                        • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                        • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                        • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                        Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        Status: Ongoing | |
                        • Will be fixed with a PR
                        | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                        Status:Ongoing | Verizon |
                        • This issue wil be closed as points moved to [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request 
                        Status: New | Orange | Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                        Status: New | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        Status: New | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                        Status: New | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38)  after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        Status: New | Verizon | DT will address this in a later PR | | +|
                        **NEW ISSUES / Discussion point** | | | | +| | |
                        • Should a company that has agreed to implement a CAMARA API, be assigned as automatic reviewer for the API contribution?
                        • Where do we track which company has agreed to implement a certain Camara API?
                        • Describe process to approve a PR
                        • What should be done if no reviewers available for certain PRs?
                        • Above points will be raiesd in next Steerco
                        | | +| **AOB** | | | | +| | | Next QoD meeting in two weeks on the Aug 26 2022 | | +
                        +# MOM-2022-08-12 + +Fri, Aug 12, 2022 10:52 PM diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..13eb39bd22953a7e85c07fa2764d74650fafff74 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09/raw.md @@ -0,0 +1,45 @@ +# Camara QoD meeting + +### Date: 09th September 2022 + +## Attendees + +* Emil Zhang (Ericsson) +* José A. Ordóñez Lucena (Telefonica) +* Eric Murray (Vodafone) +* Patrice Conil (Orange) +* ... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | | +| Issues and Pull Requests | |
                        • Issues:27[Open:15, Closed:12]
                        • Pull requests:12 [Open:8, Closed: 4]
                        | | +| **HIGHLIGHTS** | |
                        • Patrice would like to contribute a second reference implementation for QoD. To be checked with Markus Kümmerle where we can place this
                        | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        Status: Ongoing | Ericsson |
                        • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                        • Shilpa will create the new issues as agreed
                        • This later comments will be reviewed by Eric to see if this issue can be closed.
                        | | +| [#32](https://github.com/camaraproject/QualityOnDemand/issues/32) Resolving “protocolIn”/“protocolOut” with a better parameter design
                        Status: Ongoing | Ericsson |
                        • Ericsson suggests changing 'UPLINK'/'DOWNLINK' to 'FROM_UE'/'TO-UE' in 'Direction' enum. The community is happy with it. 
                        • Pull request [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is ready to merge. 
                        | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                        Status: Ongoing | DT |
                        • API version has been reset to 0.1.0. 
                        • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                        • Agreed reviewers
                          • Jose and Emil
                          • Emil has approved the PRs
                        | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution
                        Status: Ongoing | DT |
                        • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                        • No reviweres still
                        • Details of the contribution are available here 
                        • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD) [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                        | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                        Status: Ongoing | DT |
                        • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                        • No reviewers yet
                        | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                        Status: Ongoing | DT
                        Intel
                        Vodafone | Following pull requests are currently in review
                        • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                        • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                        • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                        Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        Status: Ongoing | |
                        • Will be fixed with a PR
                        | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                        Status: Ongoing | Verizon |
                        • This issue wil be closed as points moved to [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request
                        Status: Ongoing | Orange |
                        • Ericsson is willing to propose a solution too
                        | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                        Status: Ongoing | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        Status: Ongoing | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                        Status: Ongoing | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        Status: Ongoing | Verizon | DT will address this in a later PR | | +|
                        **NEW ISSUES / Discussion point** | | | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39)
                        Status: New* | Telefonica | Telefonica will address this in a later PR | | +
                        +# MOM-2022-09-09 diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..168d95785131a13936b13b69566a204907e2e078 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23/raw.md @@ -0,0 +1,61 @@ +# Camara QoD meeting + +### Date: 23rd September 2022 + +## Attendees + +* Emil Zhang (Ericsson) +* José A. Ordóñez Lucena (Telefonica) +* Eric Murray (Vodafone) +* Patrice Conil (Orange) +* Herbert Damker (Deutsche Telekom) +* Shilpa Padgaonkar (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Kevin Smith (Vodafone) +* Mahesh Chapalamadugu (Verizon) +* Mike Bowring (Spry Fox Networks) +* Sylvain Morel (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Ravi Kamalendiran (Axiata) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | | +| Issues and Pull Requests | |
                        • Issues: 29 [Open:17, Closed:12]
                        • Pull requests: 14 [Open:9, Closed: 5]
                        | | +| **HIGHLIGHTS** | |
                        • DT has created a new issue and provided a pull request for v0.8.0 of QOD API, which includes changes proposed from and discussed with several parties. The proposal combines the previous two QoD APIs into one.
                        | | +| **OPEN PULL REQUESTS** | | | | +| [#17](https://github.com/camaraproject/QualityOnDemand/pull/17)[#18](https://github.com/camaraproject/QualityOnDemand/pull/18) [#19](https://github.com/camaraproject/QualityOnDemand/pull/19) [#24](https://github.com/camaraproject/QualityOnDemand/pull/24) [#25](https://github.com/camaraproject/QualityOnDemand/pull/25) [#28](https://github.com/camaraproject/QualityOnDemand/pull/28) [#30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                        Status: In review | |
                        • Agreement to merge all artefacts related to v0.1.0 of the QoD APIs "low-latency" and "throughput" to preserve the material as reference and base within the repository history (User Story, API documentation, reference implementation code).
                        • The work will be continued on the combined single QoD API as proposed in v0.8.0, artefacts need to be updated as soon as possible.
                        | | +| [#37](https://github.com/camaraproject/QualityOnDemand/pull/37)
                        Status: In review | Ericsson |
                        • The proposed changes to v0.1.0 of stable-latency API will be superseeded by v0.8.0 (deleting the stable-latency API)
                        • The addressed issue of ambiguity of protocolIn/protocolOut parameters will not exist in v0.8.0 as these parameters are obmitted in the v0.8.0 version
                        • The pull request will be closed. The proposal of a flowinfo structure should be preserved as feature request in the backlog. Herbert will create an issue for that.
                        | | +| [#43](https://github.com/camaraproject/QualityOnDemand/pull/43)
                        Status: new pull request | |
                        • Akos presented the pull request and the related issue [#42](https://github.com/camaraproject/QualityOnDemand/issues/42)
                        • The main point is the combination of previous seperated APIs for stable latency and throughput into one combined API
                        • The existing comments were discussed. Mahesh created issues for his comments which will be addressed after implementation of v0.8.0
                        • Participants need more time for reviews, PR will kept open until next call on Oct 7
                        • DT will update the reference implementation based on proposed v0.8.0 of the API
                        | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                        Status: Ongoing | Ericsson |
                        • Introduction of a flowinfo structure should get a feature request within backlog, see discussion of PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37) above
                        • UE ID aspect is addressed within v0.8.0 with UeId structure
                        | | +| [#32](https://github.com/camaraproject/QualityOnDemand/issues/32) Resolving “protocolIn”/“protocolOut” with a better parameter design
                        Status: Ongoing | Ericsson |
                        • Ambiguity of protocolIn/protocolOut parameters is "resolved" in v0.8.0, by deleting the parameters
                        • The proposal of PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37) should be preserved for backlog
                        | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                        Status: Ongoing | DT |
                        • Will be closed with merge of [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                        | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution
                        Status: Ongoing | DT |
                        • Will be closed by merge of [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28), see above
                        | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                        Status: Ongoing | DT |
                        • Will be closed by merge of [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                        | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                        Status: Ongoing | DT |
                        • Will be closed by merge of
                          • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                          • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                          • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                        • Documentation need to be updated to reflect changes of v0.8.0
                        | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39)
                        Status: Ongoing | Telefonica | Will be closed when PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) is merged | | +| **Remaining issues not discussed due to lack of time** | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        Status: Ongoing | |
                        • Will be fixed with a PR
                        | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request
                        Status: Ongoing | Orange |
                        • Ericsson is willing to propose a solution too
                        | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                        Status: Ongoing | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        Status: Ongoing | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                        Status: Ongoing | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        Status: Ongoing | Verizon | DT will address this in a later PR | | +
                        diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f9c4758ebbe0e01f2a43268f0c3a0edb6955f15c --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07/raw.md @@ -0,0 +1,57 @@ +# Camara QoD meeting + +### Date: 7th October 2022 + +## Attendees + +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Mahesh Chapalamadugu (Verizon) +* Mike Bowring (Spry Fox Networks) +* Milan Lalovic (BT) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Ravi Kamalendiran (Axiata) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* .... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | | +| Issues and Pull Requests | |
                        • Issues: 36 [Open:18, Closed:18]
                        • Pull requests: 16 [Open: 1, Closed: 15]
                        | | +| **HIGHLIGHTS** | |
                        • Artefacts for v0.1.0 merged into main as agreed within last call, related issues closed
                        • PR #37 closed (not merged), as agreed. New issue #51 created
                        • Some clean-up done withing the repository, see PR 
                        | | +| **OPEN PULL REQUESTS** | | | | +| [#48](https://github.com/camaraproject/QualityOnDemand/pull/48) Update MAINTAINERS.MD | KDDI |
                        • Add Toshi Wakayama to sub projects maintainers
                        • Supported and no objections; merged
                        | | +| [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) Contribution of the QoD-API spec v0.8.0 | DT |
                        • Pull request was presented in last call, 14 days for feedback were agreed
                        • Joachim noted that Ericsson has started an internal review, but not able to enter the feedback yet due to vacations. Emil will enter the review during next week.
                        • If possible only urgent fixes should be done within the review, other points should be addressed as issues to be worked on after the combined API v0.8.0 is the new common base.
                        • Discussion about [code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/pull/43/files#diff-d944f3af37e3d99156930a944badae74c04f6fc2c2937657ed60ece9df752b00 "code/API_definitions/QoSProfile_Mapping_Table.md")
                          • The content of the table has not changed, just the names of the profile where replaced
                          • The note should emphasize that it is just an example how the QoS Profiles can be mapped and not binding for operators.
                          • There is a notion that guranteed bit rate (GBR) can be offered only in limited scenarios (e.g. campus). The table is currently providing only examples for relative prioritization.
                          • Proposals for changed wording (e.g. "up to xx Mbit" replaced with more use case oriented wording) are welcome.
                        | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13) "Flow Description" Mapping
                        Status: Superseded by #51 | Ericsson |
                        • Created new issue based on (closed) PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37):
                          • [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                          • Herbert will ask Emil to close #13 as superseded.
                          • UE ID aspect is addressed within v0.8.0 with UeId structure
                        | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) #23 Consistent use of the term notification URL in API docs
                        Status: Ongoibg | |
                        • Will be fixed with a later PR
                        | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        Status: Ongoing | Verizon |
                        • DT will address this in a later PR
                        | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                        Status: Ongoing | Orange |
                        • Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue
                        | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        Status: Ongoing | Vodafone |
                        • Awaiting feedback from members
                        | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                        Status:Superseded by #51? | Vodafone |
                        • As [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is not merged there is now new issue #51
                        | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                        Status: Ongoing | Orange |
                        • Ericsson is willing to propose a solution too
                        | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39) Typo in SessionInfo definition.
                        Status: PR in review | Telefonica |
                        • Will be closed when PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) is merged
                        | | +| [#40](https://github.com/camaraproject/QualityOnDemand/issues/40) Definition of flowid in NEF API AfSessionWithQosSubscription
                        Status: Discussion | Spry Fox Networks |
                        • See comment from Eric
                        | | +| [#42](https://github.com/camaraproject/QualityOnDemand/issues/42) QoD API specification version 0.8.0
                        Status: PR in review | DT |
                        • See PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) above
                        | | +| **NEW ISSUES** | | | | +| [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                        Status: new | Verizon |
                        • as discussed 2022-09-23
                        | | +| [#45](https://github.com/camaraproject/QualityOnDemand/issues/45) Need to support ability to configure fallback qos
                        Status: new | Verizon |
                        • as discussed 2022-09-23
                        | | +| [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                        Status: new | Verizon |
                        • as discussed 2022-09-23
                        | | +| [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                        Status: new | Verizon |
                        • as discussed 2022-09-23
                        | | +| [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                        Status: new | Ericsson |
                        • as discussed 2022-09-23, to preserve closed PR #37, superseding #13 (?) and #36 (?)
                        | | +| | | | | +| [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx
                        Status: new | | | | \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9e783aead4c5b21c0d9e7f6f2256319ba4fb7ecb --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21/raw.md @@ -0,0 +1,68 @@ +# Camara QoD meeting + +*21st October 2022* + +## Attendees + +* Andrew +* Assane Mbengue (Orange) +* Eric Murray (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Rocio Otiz Peña () +* Syed A Rehman (Verizon) +* Sylvain Morel (Orange) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Rec +* Housekeeping +* v0.8.0 merged - next steps +* Development branch for v0.9.0? +* Open issues and pull requests +* New issues +* Any other issues + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap & Recent Updates** | | +| |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | +| **Housekeeping** | | +| | Mailinglist: Please subscribe to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-qod](https://lists.camaraproject.org/g/sp-qod)
                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-qod@lists.camaraproject.org | +| | Team call: need to replace the current Teams link (Herbert). Will be distributed via mailing list and within the README.md +| **API Definition v0.8.0 merged** | | +| | [QoD API Spec v0.8.0](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml) merged. See [#42](https://github.com/camaraproject/QualityOnDemand/issues/42) for a summary of changes.
                        Documentation and reference implementation to be updated -> new issues. | +| | (Server) Reference implementations should go into seperate repositories , allowing multiple reference implementation without conflicts. Waiting for issue [#63](https://github.com/camaraproject/WorkingGroups/issues/63) in Commonatilities to be resolved. | +| **Branch for development of v0.9.0** | | +| | Main branch to be protected (no direct push, at least one review, codeowner review will automatically requested). For development of next iteration of the the API definition we create a branch to bundle multiple of the issues before updating main (done, new branch: [dev-v0.9.0](https://github.com/camaraproject/QualityOnDemand/tree/dev-v0.9.0)) | +| **Open Issues** | | +| | [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                        Ericsson volunteered to work on a PR. | +| | [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                        Ongoing discussion | +| | [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                        Syed will add more information +| | [#45](https://github.com/camaraproject/QualityOnDemand/issues/45) Need to support ability to configure fallback qos
                        Backlog: Alternative QoS class will require a discovery function of available QoS profiles first, see #7. Until then clear documentation what happens if requested QoS profile can not be provided by the network -> new issue | +| | [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                        Important enhancement; dependency on Commonality workgroup +| | [#41](https://github.com/camaraproject/QualityOnDemand/issues/41) Impact on Camara on the definition of flowid in NEF API AfSessionWithQosSubscription
                        Ongoing discussion; Request to add information about concrete impact on Camara QoD API | +| | [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                        Ongoing; Ericsson is willing to propose a solution | +| | [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        Request to provide a PR for the solution proposed (two optional parameters: private and public IPv4Addr) | +| | [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        DT will address this in a later PR | +| | [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        Will be fixed with a later PR | +| | [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) Add new endpoint in QoD API to request available qos_profiles
                        Backlog item | +| **NEW ISSUES** | | +| | [#56](https://github.com/camaraproject/QualityOnDemand/issues/56) Protect main branch and create branch for development of version v0.9.0
                        Rule added to repo configuration; PR [Update CODEOWNERS #55](https://github.com/camaraproject/QualityOnDemand/pull/55) created; Branch [dev-v0.9.0](https://github.com/camaraproject/QualityOnDemand/tree/dev-v0.9.0) created| +| | [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) Update of User Story | +| | [#58](https://github.com/camaraproject/QualityOnDemand/issues/58) Update of API documentation | +| | [#59](https://github.com/camaraproject/QualityOnDemand/issues/59) Document what happens if requested QoS profile can not be provided | +| | [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx | +| **Any other issue** | | +| | Next QoD community call on Nov 4th diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2e131783d2e6d0d370b213bd69e6aee3f030644c --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04/raw.md @@ -0,0 +1,73 @@ +# Camara QoD meeting + +*21st October 2022* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Diego Marí Moretón (Meta) +* Eric Murray (Vodafone) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jane Shen (Mavenir) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Maria Virtudes Briz Ruiz (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Syed A Rehman (Verizon) +* Sylvain Morel (Orange) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update maintainers.md +* Pull Request #62 - Improvement proposal for QoSProfile_Mapping_Table.md +* Update on issues +* Any other issues + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap & Recent Updates** | | +| |
                        • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                        • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                        • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                        | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-qod](https://lists.camaraproject.org/g/sp-qod)
                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-qod@lists.camaraproject.org | +| | Team call: new Teams meeting link distributed within invitation and within README.md. Time changed to UTC 13:00, due to change to wintertime in EU +| | Main branch is now protected, a merge requires at least one review by a codeowner. Codeowner will take care to involve current maintainers and invovled contributors in relevant pull request reviews. +| | Branch dev-v0.9.0 created for changes which are targeted for the next version of the API definition. Use this branch as target for change requests of the current API yaml file. +| **Update of MAINTAINERS.MD** | | +| | Jose A Ordonez Lucena resigned as maintainer and proposed Jose Luis Urien with Jesus Peña as standin as new maintainers within the subproject. Accepted without objections, change to MAINTAINERS.MD merged | +| **PR #62 - Improvement proposal for QoSProfile_Mapping_Table.md** | | +| | Thorsten presented his pull request to improve the QoSProfile_Mapping_Table with the aim to make it more understandable for developers. Comments were discussed, the PR should be continued with updates based on the discussion.
                        • The example character has to be emphasized, it is too early to agree already on numers
                        • Eric's comment can be partly addressed partly by using "statistically assured" instead of "assured" (to make clear that it isn't contractually assured)
                        • Going forward a realization of issue #7 (Add new endpoint in QoD API to request available qos_profiles) should support QoS profile definitions together with KPIs | +| **Open Issues (without backlog)** | | +| | [#61](https://github.com/camaraproject/QualityOnDemand/issues/61) QoSProfile_Mapping_Table.md should be improved:
                        • new issue, will be fixed by PR #62 discussed above. +| | [#59](https://github.com/camaraproject/QualityOnDemand/issues/59) Document what happens if requested QoS profile can not be provided
                        • to addressed within #58 | +| | [#58](https://github.com/camaraproject/QualityOnDemand/issues/58) Update of API documentation
                        • Assigned to Deutsche Telekom, will provide PR | +| | [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) Update of User Story
                        • No update | +| | [#56](https://github.com/camaraproject/QualityOnDemand/issues/56) Protect main branch and create branch for development of version v0.9.0:
                        • closed, see housekeeping above. +| | [#52](https://github.com/camaraproject/QualityOnDemand/issues/56) Solution for multiple reference implementations for QualityOnDemand:
                        • Commonality working group came to decision to move API (provider) implementations outside the subproject repository. Which means DT and Orange will have separate repositories for managing their individual QoD solutions in Camara. Details to be defined. +| | [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions:
                        • Ericsson will work on PR, but current priority on #38. | +| | [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                        • No update; ongoing discussion | +| | [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                        • No update; Syed will add more information +| | [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                        • No update; Important enhancement; dependency on Commonality workgroup +| | [#41](https://github.com/camaraproject/QualityOnDemand/issues/41) Impact on Camara on the definition of flowid in NEF API AfSessionWithQosSubscription
                        • Mike added further explanation, community requested to discuss if this issue impacts Camara QoD directly. 3GPP members to consider to take it into 3GPP. | +| | [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                        • Ongoing; Ericsson is working on a solution proposal | +| | [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                        • Solution proposal from Eric is supported; he will work on a PR | +| | [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                        • No update: DT will address this in a later PR | +| | [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                        • No update; Need to be fixed with a later PR | +| **New Issues** | | +| | [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx | +| **Any other issue** | | +| | Next QoD community call on Nov 18th, UTC 13:00, CET 14:00 diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5849b2d5415f545cc170c9b45a60ebddb64f96ea --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02/raw.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +*December 2nd, 2022* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Diego Marí Moretón (Meta) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Open Pull Requests (3) +* New Issues +* Next calls + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| **Recap & Recent Updates** | | +| |
                          • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                          • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                          • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                          | +| **PR #71 - Update qod api documentation to 0.8.0** | | +| |
                          • Thanks to Thorsten for his detailed review of the documentation. Most comments/suggestions are committed, result is fine for Thorsten
                          • Some comments need to be addressed in API definition & documentation (=> issue for v0.9.0)
                          • Agreement to commit the current version as soon as possible to have a base for further improvements. Jose Luis Urien will do a final review (Update: done & minor suggestion committed).
                          • After merge of the current PR Herbert will initiate a minor editorial PR, mainly to split up the current huge line 99 to ease later reviews
                          • Afterwards furhter fixes can be proposed
                          | +| **PR #73 - Reduce to one example QoSProfile\_Mapping\_Table.md** | | +| |
                          • No objection to the proposal in issue #72 and PR #73
                          • Jose Luis Urien will do a final review from TEF perspective (Update: Suggestion to be more aligned with short term implementions done & committed)
                          | +| **PR #67 - Introduce 'qosStatus' and corresponding notification event to fix issue #38** | | +| |
                          • The presentation done in last call by Emil was helpful for the understanding of the PR
                          • Emil updated the PR according to the comments
                          • Reviews by TEF (Jose Luis Urien), KDDI (Toshi) and DT (as codeowner) to be done
                          | +| New Issues | | +| |
                          • Commonalities has agreed on API guidelines. Jose Luis Urien will create an issue and PR for version 0.9.0
                          | +| **Next Calls** | | +| |
                          • Next QoD community call on Friday, Dec 16th, UTC 13:00, CET 14:00
                          • Call on Dec 16th will be skipped
                          • First call in 2023 on Friday, January 13th, UTC 13:00, CET 14:00
                          | diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..342d846a644079c32368d6ddd7d3a44080c3e98b --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13/raw.md @@ -0,0 +1,56 @@ +# Camara QoD meeting - MOM-2023-01-13 + +*Januar 13th, 2023* + +## Attendees + +* Andrew +* Babu Narayan (?)(Nabstract) +* Diego Marí Moretón (Meta) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Release planning +* Issues to "fix" 0.8.0 +* Review of open issues and PRs (esp. [#67](https://github.com/camaraproject/QualityOnDemand/pull/67), [#34](https://github.com/camaraproject/QualityOnDemand/issues/34), [#52](https://github.com/camaraproject/QualityOnDemand/issues/52)) +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| Release Planning | We need a release and branching strategy for our sub projects:
                          • Releases to be done with Github release feature
                          • Current status of main to be "released" as v0.8.0
                          • As long as we are in v0.x.x backward compatibility is not mandatory, current status is "alpha"
                          • Issues and PRs with small (bug) fixes (see next agenda item) to be addressed short-term and to be released as v0.8.1
                          • Issues and PRs with larger changes (e.g. #67, #34) will go into v0.9.0 ("alpha2" release)
                          See also issue [#118](https://github.com/camaraproject/WorkingGroups/issues/118) in Commonalities and the related PR with draft for versioning guidelines. | +| Issues for "fix" release v0.8.1 | Several issues and PR are addressing smaller typos, bugs, missing error codes etc:
                          • PR [#77](https://github.com/camaraproject/QualityOnDemand/pull/77) \- Fixed couple of typos =\> to be merged \(UPDATE: done\)
                          • Issue #83 - Internal server error 500 missing for GET & DELETE procedures=> addressed with PR [#86](https://github.com/camaraproject/QualityOnDemand/pull/86) (UPDATE: merged after review)
                          • Issue [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) \- Consistent usage of notificationUri vs notificationUrl=\> will be addressed by DT \(UPDATE: done with new issue [#88](https://github.com/camaraproject/QualityOnDemand/issues/88) and PR [#89](https://github.com/camaraproject/QualityOnDemand/pull/89))
                          • Issue [#84](https://github.com/camaraproject/QualityOnDemand/issues/84) \- \[qod\-api\.yaml\]: IPv6\-object will be generated instead of a String=\> to be discussed if this is a short\-term fix\, probably not
                          • Issue [#81](https://github.com/camaraproject/QualityOnDemand/issues/81) \- Introducing error code 501 "Not Implemented"=\> DT will provide PR
                          • Potential further minor fixes, e.g. in documentation
                          | +| PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67) |
                          • Open conversations from review discussed => can be marked as resolved (Emil)
                          • PR need to be rebased against main branch after fix release v0.8.1 is done
                          • Documentation need to be updated according to the changes (within PR or in separate one?)
                          | +| Issue [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) |
                          • PR will be provided by Eric after PR #67 is done
                          | +| Issue [#52](https://github.com/camaraproject/QualityOnDemand/issues/52) |
                          • Two new repos created for provider implementation (PI)
                          • [QualityOnDemand_PI1](https://github.com/camaraproject/QualityOnDemand_PI1) for DT’s provider implementation
                          • [QualityOnDemand_PI2](https://github.com/camaraproject/QualityOnDemand_PI2) for Orange’s provider implementation
                          | + +## PRs that can be merged + +* PRs for fixes as listed above after being reviewed + +## Issues that can be closed + +* Issue [#52](https://github.com/camaraproject/QualityOnDemand/issues/52) can be closed, repos for provider implementations created + +## AOB + +\* Next call is on January 27th. \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b62d3d3cd07f9217e55aa2104f6f27bc7deb1984 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27/raw.md @@ -0,0 +1,70 @@ +# Camara QoD meeting - MOM-2023-01-27 + +*Januar 27th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Albert Wang (Huawei) +* Andrew +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Jignesh Sorathia (Spry Fox Networks) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Release v0.8.0 +* Release v0.8.1 +* Review of open PRs and issues +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| Release v0.8.0 | Release 0.8.0 done as agreed in last call.
                          Release in GitHub: [https://github.com/camaraproject/QualityOnDemand/releases/tag/v0.8.0](https://github.com/camaraproject/QualityOnDemand/releases/tag/v0.8.0)
                          Release branch: [https://github.com/camaraproject/QualityOnDemand/tree/release-0.8.0](https://github.com/camaraproject/QualityOnDemand/tree/release-0.8.0)
                          Going forward we want to follow [Draft versioning guidelines doc](https://github.com/camaraproject/WorkingGroups/pull/123) (need to be finalized in Commonalities)
                          Open issue/discussion: [API spec files and versioning](https://github.com/camaraproject/WorkingGroups/discussions/137) | +| Release v0.8.1
                          Issue #105
                          PR #106 | Issues addressed:
                          • PR [#77](https://github.com/camaraproject/QualityOnDemand/pull/77) \- Fixed couple of typos
                          • Issue #83 - Internal server error 500 missing for GET & DELETE procedures=> addressed with PR [#86](https://github.com/camaraproject/QualityOnDemand/pull/86)
                          • Issue [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) \- Consistent usage of notificationUri vs notificationUrldone with new issue [#88](https://github.com/camaraproject/QualityOnDemand/issues/88) and PR [#89](https://github.com/camaraproject/QualityOnDemand/pull/89))
                          • Issue [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) \- Update API documentation
                          PR with update of changelog: [#106](https://github.com/camaraproject/QualityOnDemand/pull/106) ... ready to be merged (and done). | +| PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67)
                          Issue [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) | [Introduce 'qosStatus' and corresponding notification event to fix issue #38](https://github.com/camaraproject/QualityOnDemand/pull/67)
                          • Open conversations from review marked as resolved (Emil)
                          • **Target release v0.9.0**
                          • **PR need to be rebased against main branch** **(branch dev-0.9.0 outdated and not in line with upcoming versioning guidelines)**
                          • Documentation need to be updated according to the changes - within this PR or in separate one?
                          • Thorsten will approach Emil as author of the PR with the above action items.
                          | +| PR [#104](https://github.com/camaraproject/QualityOnDemand/pull/104) | [Align error format with Commonalities guidelines #104](https://github.com/camaraproject/QualityOnDemand/pull/104)
                          • **Target releaase v0.9.0**
                          • Additional reviewer: Patrice, Eric
                          • To be merged as soon as possible (before #67), to get new error objects already in correct format
                          | +| Issue [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) | [Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34)
                          • PR will be provided by Eric after PR #67 is done
                          • **Target release: v0.9.0 - in general we will accumulate multiple changes within the next release, as there is currently no interest to implement an interims release**
                          | +| Issue [#107](https://github.com/camaraproject/QualityOnDemand/issues/107) | [QoD Provider Implementation proposal - From Spry Fox Networks](https://github.com/camaraproject/QualityOnDemand/issues/107)
                          • Slides presented by Ramesh are attached to the issue
                          • Herbert will create the repo QualityOnDemand\_PI3 and will initially add Ramesh as code owner
                          • Issue can be closed afterwards
                          | +| Issue [101](https://github.com/camaraproject/QualityOnDemand/issues/101) | [List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (DT)
                          • Recognized as an important functionality; DT is asked to provide a PR
                          • Alignment with Design Guidelines necessary (pagination)
                          | +| Issue [97](https://github.com/camaraproject/QualityOnDemand/issues/97) | [Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/issues/97)
                          • Analysis done by Jose Luis Urien
                          • Property names in snake\_case => Issue #90
                          • Error format => PR #104
                          | +| Issue [#96](https://github.com/camaraproject/QualityOnDemand/issues/96) | [Versioning of OAS yaml file in main branch between releases](https://github.com/camaraproject/QualityOnDemand/issues/96)
                          • Waiting for Commonalities if and how API will should be versioned (independent of release versioning of the project)
                          • **As interim solution we bump version number of QoD-API.yaml in main to 0.9.0-wip** (done)
                          • Further discussion about versioning within Commonalities
                          • Issue can be closed
                          | +| Issue [#90](https://github.com/camaraproject/QualityOnDemand/issues/90) | [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90)
                          • Request from Commonalities working group
                          • First proposal for QoD from Jose Luis Urien
                          • **Action item for all participants: Give feedback and opinions on the terminology and proposals for alternative names within the issue**
                          • **Dedicated agenda item within next call**
                          | +| Issue [#85](https://github.com/camaraproject/QualityOnDemand/issues/85) | [Content type for http error response should be of type "application/problem+json"](https://github.com/camaraproject/QualityOnDemand/issues/85) (SfnUser)
                          • Discussed, can be closed. Further discussion within Commanalities.
                          | +| Issue [#84](https://github.com/camaraproject/QualityOnDemand/issues/85) | [\[qod-api.yaml\]: IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/issues/84) (DT)
                          • No change on API level, but mitigations in implementations?
                          • DT will check for alternatives
                          | +| Issue [#81](https://github.com/camaraproject/QualityOnDemand/issues/81) | [Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/issues/81) (DT)
                          • Initial PR closed, waiting for PR #104 first
                          • 4xx error code more suitable in most cases
                          • **Target release v0.9.0**
                          | +| Issue [#80](https://github.com/camaraproject/QualityOnDemand/issues/80) | [Inconsistencies in the spec](https://github.com/camaraproject/QualityOnDemand/issues/80) (SfnUser)
                          • Discussed, inconsistent error messages around UEId can be addressed together with issue #34 (Eric)
                          • Issue can be closed
                          | +| Issue [#75](https://github.com/camaraproject/QualityOnDemand/issues/75)
                          Issue [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) | [Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/issues/75) (CapGemini)
                          [Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) (DT)
                          • Both issue are addressing same topic
                          • Solution proposal needed
                          | +| Issue [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) | [need to include support for /PUT sessions](https://github.com/camaraproject/QualityOnDemand/issues/47)
                          • Stale issue
                          • Will be changed to backlog
                          | +| Issue [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) | [GET /sessions is missing status information](https://github.com/camaraproject/QualityOnDemand/issues/46)
                          • Addressed within PR #67 (session life cycle and possible states)
                          • Can be closed when PR #67 is done
                          | + +## PRs that can be merged + +* PR #106 [CHANGELOG.md update for v0.8.1 release](https://github.com/camaraproject/QualityOnDemand/pull/106) + +## Issues that can be closed + +* Issue #105 [Release of v0.8.1 (fix release)](https://github.com/camaraproject/QualityOnDemand/issues/105) +* Issue #96 [Version of quod-api.yaml changed to 0.9.0-wip in main] +* Issue #107 [Repo QualityOnDemand created] +* Issue #80 +* Issue #85 + +## AOB + +* Next call is on February 10th. + * Dedicated agenda item: issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7be408f5c17afb339f9943125258ebb2b5f0c810 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10/raw.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - DRAFT MOM-2023-02-10 + +*February 10th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone)? +* Theohar (Hari) Konomi (TELUS) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Shutting Qing (Huawei)? +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Further open Issues +* AOB + +## Open PRs + +* PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67) [Introduce 'qosStatus' and corresponding notification event to fix issue #38](https://github.com/camaraproject/QualityOnDemand/pull/67) + * Rebased to main, final review done and merged. + * Ready to merge? + * Fixed issues #38 and #46 + * Documentation need to be updated according to the changes => new issue +* PR [#104](https://github.com/camaraproject/QualityOnDemand/pull/104) [Align error format with Commonalities guidelines #104](https://github.com/camaraproject/QualityOnDemand/pull/104) + * Finally reviewed and ready to merge. + * There might be later additional alignment demand, e.g. when [WorkingGroups/issues/151](https://github.com/camaraproject/WorkingGroups/issues/151) is decided + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Notes from the discussion are documented in [comment](https://github.com/camaraproject/QualityOnDemand/issues/90#issuecomment-1427893395) +* Disucssions and polls will be opened by Herbert as noted. + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +Discussion: +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * DT will do a PR +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * and related issue [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * DT is currently testing a solution and might make a proposal here afterwards + * Further proposals are also welcome +* [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + * Eric will create a PR based on his proposal and the discussion + * He will consider to have private\_ipv4\_address and public\_ipv4\_address as top-level parameters in the object, both with potential additional information which the API consumer can provide to make them unambiguous + +## AOB + +* Next call is on February 24th. \ No newline at end of file diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fdf39332c7e0012fad7f228738002bd1044ed0af --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24/raw.md @@ -0,0 +1,98 @@ +# Camara QoD meeting - MOM-2023-02-24 + +*February 24th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mayur Channegowda (Vodafone) +* Mihai Lazar (Dell) +* Mike Bowring (Spry Fox Networks) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Shuting Qing (Huawei) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* Issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Issue #34 [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* (NEW) [PR #124 Qod profiles](https://github.com/camaraproject/QualityOnDemand/pull/121) +* Further new and open Issues +* AOB + + +## Updates +* Provider implementation (DT) in review: [Implementation of 0.8.0 version](https://github.com/camaraproject/QualityOnDemand_PI1/pulls) + * PR will be merged as there are no comments so far +* Fix PR by Jose merged: [fix/restore-QosStatus-schema #116](https://github.com/camaraproject/QualityOnDemand/pull/116) + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Discussion on the polls (please vote before the call or during the discussion): + * [Preferred alternative for "ueID"? - device_info, device, or user_device](https://github.com/camaraproject/QualityOnDemand/discussions/117) + * No clear tendency yet, please continue to vote + * [Preferred alternative for "externalID" - external_id, network_access_identifier, ...?](https://github.com/camaraproject/QualityOnDemand/discussions/118) + * Clear tendency for "network access identifier" + * [Preferred alternative for "asId" - app_server_info, app_server, application_server, ...?](https://github.com/camaraproject/QualityOnDemand/discussions/119) + * Tendency towards "application server" + * [Preferred alternative for "uePorts"/"asPorts"? - *_ports, *_ip_ports, ...](https://github.com/camaraproject/QualityOnDemand/discussions/120) + * Tendency towards "_ports" over "_ip_ports" + * **Polls will kept open unti Friday, March 3rd, noon (UTC), please continue to provide your vote if not yet done** +* Sidenote: (camelCase vs snake_case) ongoing in Commonalities: https://github.com/camaraproject/WorkingGroups/issues/157 + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + +* Pull Request [#123 Update UeId definition in qod-api.yaml](https://github.com/camaraproject/QualityOnDemand/pull/123) +* Please provide your comments within the open PR (will be kept open at least until Friday March 3rd, and then until a cool down of 2 business days happened) +* Proposal to change paramater "port" with public IPv4 address into "public port" (Update: done by Eric) + +## PR [#124 Qod profiles](https://github.com/camaraproject/QualityOnDemand/pull/121) + +* Discussion: PR on backlog item #7 ... proposing a function to create QoS profiles + * The discussion started on the PR should first be done within one or two issues + * A dynamic creation of new QoS profiles shouldn't be offered to developers, but a discovery of QoS profiles offered by a network operator would be very helpful + * Also the possibility to get the QoS profiles as a machine readable object structure. The paramaters need an intensive discussion + * The current PR will be closed by Randy and he will summarize the discussion and learnings in one or two new issues which will probably superseed the existing issue #7. + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +New issues: +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * DT asked to do the PR + +As of last call: +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-02-24: no update +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * DT will do a PR +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * and related issue [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * DT is currently testing a solution and might make a proposal here afterwards + * Further proposals are also welcome + +## AOB + +* Next call is on March 9th diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..526249a7a46e4b3d240e7dc2f87e42e5948f4b90 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10/raw.md @@ -0,0 +1,89 @@ +# Camara QoD meeting - MOM-2023-03-10 + +*March 10th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Frimann (Ericsson) +* Jignesh Sorathia (Spry Networks) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* Issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* PR [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Further new and open Issues +* AOB + +## Updates +* Lot of interest in Camara and GSMA Open Gateway on MWC in Barcelona. Several showcases with QoD API. + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* **Request for all:** please review the definition proposed by Jose in https://github.com/camaraproject/QualityOnDemand/issues/90#issuecomment-1456609800. Jose will contribute the resulting definitions at latest on March 15th to Commonalities. +* New PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) prepared to execute the changes within API definition and documentation. Will be merged after the final decision about snake_case vs camelCase in Commonalities + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + +* Pull Request [#123 Update UeId definition in qod-api.yaml](https://github.com/camaraproject/QualityOnDemand/pull/123) closed as the current discussion requires a new proposal. See continued discussion within the issue for Eric's proposal. +* Emil presented his discussion paper with concept and alternative API design, see [Discussion paper for Issue#34 and PR#123 #127](https://github.com/camaraproject/QualityOnDemand/pull/127) + * Eric asked to add a third scenario where both local/private UE address and observed/public UE address are collected on the device app and used within the QoD session create + * We will use the agreed term device instead of UE + * A decision between local/observed vs private/public IP might need a vote + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### New issues: + +* [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) + * Created by Randy as discussed within last call based on (now closed) PR #121 + * Some example QoS profiles would be helpful + * Discussion to be continued within the issue + +### Open issues: + +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * PR to be done (DT) +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-03-10: no update +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) + +### Issues closed / to be closed: + +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * PR done and merged +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * To be closed as duplicate to [#31 Ensure secure handling of callback URL], actual discussion in #31 + +## AOB + +* Next call will be on March 24th, 2 PM CET / 13:00 UTC (Please note: Europe will change on March 26th - after the next call - to daylight saving time) +* Agenda proposal will be created if possible at least one day in advance of the call as draft pull request diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..238ab8ef83368131939f0a8bf8c9b9edb8ed35b6 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24/raw.md @@ -0,0 +1,101 @@ +# Camara QoD meeting - MOM-2023-03-24 + +*March 24th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Gareth Williams (GSMA) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Shuting Qing (Huawei) +* Syed A Rehman (Verizon) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) +* Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Issue/Discussion [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open Issues +* AOB + * Next call + * Planning towards release v0.9.0 + +## Updates +* New/additional maintainer from Verizon: Mahesh Chapalamadugu [PR 132](https://github.com/camaraproject/QualityOnDemand/pull/132) + +## PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) +* Based on the decisions in [#90](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Akos and Emil offered to do a review before merge +* PR will be kept open until Wednesday March 29th +* It's important to merge the PR soon as a prerequisite for the next PRs (the changes are across the complete YAML and documentation and merge conflicts would unavoidable) + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Emil presented and explained the added scenario(s) within [UE IP address and ports in QoD.PA3.pdf](https://github.com/camaraproject/QualityOnDemand/files/11013180/UE.IP.address.and.ports.in.QoD.PA3.pdf) (attached at issue comment) +* Proposal is to ask developers to add all attributes they can observe (easily) and not make the minimum set dependent on network configurations +* Device port(s) might be neither helpful for device identification nor for (current simple) flow description - could be omitted completetly +* Port(s) should to with the IP addresses into the Device object - Emil will change the proposal accordingly +* Discussion to be continued within the issue (but should be concluded soon, see "Release Planning" in AOB) + +## Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Randy presented the updated proposal +* Throughput/bandwidth replaced with neutral term "rate" +* Q: intended for mobile and/or fixed - A: both +* Burstrate needs a description/definition of a burst (e.g. duration, percentage of time etc) +* Discussed if it would make sense to add a "type" of profile ('best effort' vs 'guaranteed') in addition to the attribute which allow to define theses characteristics (e.g. for easier search). Emil will have a closer look and might make a proposal into this direction. Term "GBR" should not be used as telco and mobile specific +* There was also a request to support (backwards compatibility with) the current QoS Profile enum + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### New issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * As per discussion on [camaraproject/WorkingGroups#61](https://github.com/camaraproject/WorkingGroups/issues/61), DT will provide basic tests with Cucumber framework using Java and Maven implementation + +### Open issues: + +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * PR to be done (DT, after PR #129 is merged) +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and #129 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-03-24: no update +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) - therefore on hold in QoD + +### Issues closed / to be closed: + +* none + +## AOB + +* **Next Call** + * We will skip April 7th (Good Friday) + * The next call will be therefore on April 21st, 2 PM CEST / 12:00 UTC +* **Planning for release v0.9.0** + * Aim is to have a release of v0.9.0 before summer / within June + * There should be a release candidate (pre-release in Github terms) 4-6 weeks in advance to give implementators a chance to identify potential bugs/fixes necessary for the release, and adapt documentation and test cases + * The solutions for the two issues [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) and [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) should be at least part of the release v0.9.0 + * Herbert will create an issue with a proposed planning for the release (milestones and content) + diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0eaa0094028bc1a27d993ca3c33852e93314042f --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21/raw.md @@ -0,0 +1,83 @@ +# Camara QoD meeting - MOM-2023-04-21 + +*April 21st, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Chris Corcimiglia (CableLabs) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Mihai Lazar (Dell) +* Nuno Emanuel Rodrigues (Nos) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) +* PR for [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* PR for [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open PRs and Issues +* AOB + * Next call + +## Updates +* Templates for issues and PRs agreed in Commonalities (see [Proposed Github issue and pull request templates #174](https://github.com/camaraproject/WorkingGroups/pull/174)) +* New issue: [Orga: Enable use of Issue and PR templates in QoD sub project #140](https://github.com/camaraproject/QualityOnDemand/issues/140) + +## Release Planning v0.9.0 +* Agreed as described in [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) +* Content will be the PR described below, target is to start the final review with the next call on May 5th +* Discussion of issue for v0.10.0 can start soon + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34) +* PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) +* Please review the PR soon to allow resolving of comments before next call, comments to be documented within the PR +* Herbert will create votes (discussion items) for the remaining terminology discussions + +## Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* Please review the PR soon to allow resolving of comments before next call, comments to be documented within the PR + +## Further open PRs issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### Further open PRs and issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * Draft PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) + * Completion of the the PR planned for next week +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Will not be fixed, see [comment in issue](https://github.com/camaraproject/QualityOnDemand/issues/115#issuecomment-1515994592), to be closed +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * Done with the (merged) PRs #104 and #129, to be closed +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-04-21: no update, stale issue +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) - therefore on hold in QoD + +### Issues closed / to be closed: + +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/issues/97) +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + +## AOB + +* The next call will be on May 5th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bcb659503ff397b50e6b1556d025d1f9ce1d3aab --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05/raw.md @@ -0,0 +1,81 @@ +# Camara QoD meeting - MOM-2023-05-05 + +*May 5th, 2023* + +## Attendees (Incomplete) + +* ... +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Nuno Emanuel Rodrigues (Nos) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates and housekeeping +* PR for [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* PR for [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open PRs and Issues +* AOB + +## Updates and housekeeping + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * "Content will be the PRs described below, target is to start the final review with the next call on May 5th" + * Target is to have final review versions of PRs below until May 12th in Github + * New issue on documentation [Add documentation into API definition for release v0.9.0 ](https://github.com/camaraproject/QualityOnDemand/issues/144) + * Jose Luis Urien Pinedo volunteered, issue assigned + * Status of discussion within Commonalities on [Update API guidelines to add subscription/notification/event.md #173](https://github.com/camaraproject/WorkingGroups/pull/173)? => required for our issue [Ensure secure handling of callback URL #31](https://github.com/camaraproject/QualityOnDemand/issues/31) + * Rafal: aim in Commonality is to have final review/merge within next week. + + +## Issue #34 / PR #139 +* Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34) +* PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) +* Results of discussions/votes: + * [Vote: DeviceIpv4Addr object properties (from PR #139)](https://github.com/camaraproject/QualityOnDemand/discussions/141): Option 1 decided: `publicAddress`, `privateAddress` & `publicPort` + * [Vote: Rename of devicePorts property of CreateSession object](https://github.com/camaraproject/QualityOnDemand/discussions/142): decision to keep `devicePorts`for now +* Eric will update the PR based on the results, then ready for final review + +## Issue #124 / PR #138 +* Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* For discussion results see [PR comment](https://github.com/camaraproject/QualityOnDemand/pull/138#issuecomment-1537887796) + + +## Further open PRs issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### Further open PRs and issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) + * PR is in review - discussion will happen there. + +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-05-05: no update, stale issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) + * Result in Commonalities expected next week, impact on QoD API should go still into v0.9.0 if possible. + +### Issues closed / to be closed: + +* n/a + +## AOB + +* The next call will be on May 19th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..428a0847b1149ce23028557f539ce333862ef0ff --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19/raw.md @@ -0,0 +1,107 @@ +# Camara QoD meeting - MOM-2023-05-19 + +*May 19th, 2023* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Karthik Sethuraman (?) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates and housekeeping +* Adding new maintainer +* Open PRs for v0.9.0 +* Further issues to be addressed for v0.9.0? +* Other issues (w/o backlog) +* Issues to be pulled from backlog for next release? +* AOB + +## Updates and housekeeping + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * Plan for today: + * Final decision which PRs will be merged for v0.9.0 (if not already done) + * Creation of prerelease of v0.9.0 (v.0.9.0-rc1, "Release Candidate") + * Purpose of the release candidate is that implementations can be started in order to identify bugs or other implementation obstacles + * For that the API definition and its structure is important. Descriptions can be changed independent of that. + * Note: PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) is already merged + + +## Adding new maintainer + +* Proposal to add Ramesh Shanmugasundaram (Spry Fox Networks, @sfnuser) to the list of Maintainers [PR](https://github.com/camaraproject/QualityOnDemand/pull/148) +* Unfortunately missed to address in the call ... current maintainers should vote with their approval to the [pull request #148](https://github.com/camaraproject/QualityOnDemand/pull/148) + +## PRs for v0.9.0 + +### Issue #125 / PR #138 +* Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* Discussion + * Q: can the current profile names (QOS_E, QOS_S, QOS_M, QOS_L) continued to be used. A: yes, that was the intention of keeping the format of QoSProfileName flexible. + * Three smaller change request to the PR raised (Randy noted them down). Including dealing with the warnings raised by swagger. Jose will help with these, as he has solved them also within PR #151 +* Jose, Eric, and Ramesh should approve that there comments are addressed +* Further comments on the descriptions to be postponed after the merge (via new issues). Target for now is to get the structure into the release candidate. +* Target is to merge within next week + +### Issue #144 / PR #151 +* Issue [Add documentation into API definition for release v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/144) +* PR [doc/update-spec-doc-issue-144 #151](https://github.com/camaraproject/QualityOnDemand/pull/151) +* New PR by Jose (@jlurien) +* Reviews by Randy, Emil and all other interested to review +* Review if possible within next week (until May 26th), so that Jose has a chance to addresse the comments before the next call. + +### Issue #133 / PR #134 +* Issue [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) +* PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) +* Two approvals available, no open review comments +* Ready to merge. + * Note: Corrections can be done until final relase of v0.9.0 via issues and PRs, extensions via issues for later releases + + +## Further issues to be addressed still in v0.9.0? + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Content discussion within Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) seems to have concluded. UPDATE: issue is fixed, the respective [PR #173](https://github.com/camaraproject/WorkingGroups/pull/173) has been merged + * Herbert will ask DT team to check for the needed changes + +* [#146 Format 'ipv4' is more restrictive than the pattern in Data Type 'Ipv4Address'](https://github.com/camaraproject/QualityOnDemand/issues/146) + * Agreed solution is to omit the format strings "ipv4" and "ipv6" from the definitions of Ipv4Address and Ipv6Address + * Thorsten will create the PR for it (UPDATE: see [PR #153](https://github.com/camaraproject/QualityOnDemand/pull/153)) + + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * 2023-05-05: no update, stale issue + * 2023-05-19: close issue as won't fix + + +## Issues to be pulled from backlog for next release? + +* see [https://github.com/camaraproject/QualityOnDemand/labels/QoD-backlog](https://github.com/camaraproject/QualityOnDemand/labels/QoD-backlog) + +### Issues closed / to be closed: + +* Issue #84, see above + +## AOB + +* Herbert will add a sentence within the README.md of the repository about the status of content in main (= work in progress, not yet released) +* The next call will be on June 2nd, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2a51f45825291ee2c6dfbb06d0a2ecd6726cfbf8 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02/raw.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - MOM-2023-06-02 + +*June 2nd, 2023* + +## Attendees + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jan Frimann (Ericsson) +* Jesus Gonzalez Tejeria (Vay) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Update and housekeeping +* PRs for v0.9.0 +* Further open issues (w/o backlog items) +* AOB + +## Updates and housekeeping + * New participant in the round: Jesus Gonzalez Tejeria from vay.io + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * We are behind the planned schedule ... we need to get the pending PRs merged as soon to be able to create the release candiate + * Update of README.md (PR #156) - ready to be merged after minor update for readability + +## PRs for v0.9.0 + +### Issue #125 / PR #138 +* Existing comments addressed, syntax linting done +* Final reviews to be done until end of Tuesday June 6th - the PR need to be merged to allow to resolve conflicts in PR #151 + +### Issue #144 / PR #151 +* One review so far, more would be preferred +* Added Emil and Randy who volunteered last time as reviewers, but all others are also invited to review +* Jose will update the PR after #138 is merged (to resolve conflicts) + +### Issue #133 / PR #134 +* Merged as agreed, issue #133 closed + +### Issue #154 and #157 / PR #155 +* Two proposals, no clear preference how to resolve https://github.com/camaraproject/QualityOnDemand/pull/155#discussion_r1212798906, tendency towards option 2 (more compact, compatible with swagger 2.0) +* Tendency to remove apiKey completely from API spec (and resolving issue #157 with that), Akos will check with Orange +* Akos will address the open points beginning of next week + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * moved into backlog, as not fully addressed by updated notificiation handling +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * Supported as a good idea, Randy offered to make a proposal/pull request (Herbert will support if admin rights needed) + * Note: there is in the meantime also an issue within Commonalities (https://github.com/camaraproject/WorkingGroups/issues/232), both authors are connected + +### Issues closed / to be closed: + +* Issue #146 as done by PR #153 + +## AOB + +* Please help to get the release candidate v0.9.0 created (should be done within next call) +* The next call will be on June 16th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..410678d1010683ab57e1bda8e47b5ce7188fcffe --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16/raw.md @@ -0,0 +1,110 @@ +# Camara QoD meeting - MOM-2023-06-16 + +*June 16th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* PR #151 - doc/update-spec-doc-issue-144 +* Preparation for v0.9.0-rc prerelease +* Issue #158 - Add linting GitHub actions +* Discussion of backlog issues, scope of release after v0.9.0 +* AOB + +## Updates and housekeeping + * Merged between the calls as agreed: + * PR [#163 Add oauth authorizationCode security to sensible endpoints](https://github.com/camaraproject/QualityOnDemand/pull/163) - fixed #161 + * PR [#155 Aligned notifications with guideline](https://github.com/camaraproject/QualityOnDemand/pull/155) - fixed #154 and #157 + +## Preparation for v0.9.0-rc prerelease + * Almost ready to create v0.9.0-rc, the release candidate of v0.9.0 + * Steps to create the release (similar for all releases) + * PR with updates of CHANGELOG.md and change of version in .yaml to v0.9.0-rc (instead v0.9.0-wip) + * Will be created by Herbert + * Review until eob Tuesday June 20th + * Merge commit of the PR will be tagged as v0.9.0-rc + * Via Github release feature, as pre-release in this case + * Release description will be copied from Changelog + * Proposal: no release branch for the pre-release + * Next commit after the release is setting the version within .yaml again to v0.9.0-wip + * Two or four weaks later the actual release v0.9.0, time to be used for + * Bug fixes, e.g. found by implementation teams + * Updates of documentation, e.g. clarifications, editorial fixes etc. + +## PR [#151 - doc/update-spec-doc-issue-144](https://github.com/camaraproject/QualityOnDemand/pull/151) + * PR is rebased to current main, comments are addressed + * Previous .md documentation file removed to avoid inconsistencies + * Discussion about QosStatus enum: + * The issue came up within comment in PR #155, but not solved there + * Option 1: use same enum within response bodies and events, explain differences (not all values will be currently used in events) in documentation + * Option 2: split current QosStatus enum in two, a new model "EventQosStatus" to be used within notification events + * Decision to go with option 2, as more flexible for future extensions + * Update: new PR [#167](https://github.com/camaraproject/QualityOnDemand/pull/167) created by Jose, will be merged on Monday + * PR merged and issue #144 closed + +## Issue [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * In work by Randy, PR to be expected for next call + * Cooperation with issue in Commanalities [#232 Extend the API guidelines with a concrete ruleset](https://github.com/camaraproject/WorkingGroups/issues/232) + * QoD sub project once again as pioneer + +## Discussion of backlog issues, scope of release after v0.9.0 + +* Definition of scope of v0.10.0 (or v1.0.0) should include input from the "Product Team" (in GSMA Open Gateway?) + * Process how demand from product perspective can come into the scope definition of next release to be clarified + * Jose will invite TEF colleague into next call to introduce the Product team + * Objective of the team is to ensure that defined APIs will be implemented by as many operators as possible with the same coverage of the API features + * Consensus that the ratio between value for developers/API consumers vs implementation effert for operators is an important criteria for the decisions which enhancements should go into the next release + * Beside "product requirements" there could be technical requirements which need to be addressed + +* General notion that the next release should have a focus on stability and should avoid breaking changes + +* Discussion of the issues currently within backlog + + * [#7 Add new endpoint in QoD API to request available qos_profiles](https://github.com/camaraproject/QualityOnDemand/issues/7) + * Base functionality done in v0.9.0, remaining functionality in #147 and #166 + * Original issue to be closed
                          + * [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * Security issue potentially not completely addressed within v0.9.0, Akos will create a new issue with the remaining points + * [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/pull/45) + * Functionality of NEF in Rel 16/17, unclear if implementions within operator cores are available + * Product demand to be clarified + * [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + * Demand and implementation effort to be clarified + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/101) + * Requests from developers known (to recover session IDs) + * Implementation be possible based on clientId used in OAuth authentication + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/pull/147) + * Derived from [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) above + * Demand and implementation effort to be clarified + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/pull/166) + * Derived from [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) above + * Demand most likely, implementation effort to be clarified + +### Issues closed / to be closed: + + * Issue #144, fixed by #151 + * Issue #7, remaining issues within #147 and #166 + +## AOB + +* Topics for next call + * Status of release (candidate) v0.9.0 + * PR for #158 + * Discussion of product team request for next release +* The next call will be on June 30th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c3b6f7fa2a627cfb4a83571c7f950e5a61126e95 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30/raw.md @@ -0,0 +1,46 @@ +# Camara QoD meeting - MOM-2023-06-30 + +*June 30th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Discussion + +* Feedback to v0.9.0-rc … any bugs detected, when we are ready to do the actual release? + * Merged bug fix: priority integer format to int32 by @jlurien in https://github.com/camaraproject/QualityOnDemand/pull/175 + * Issue #174 agreed to change, Patrice will create the PR for it (update: see https://github.com/camaraproject/QualityOnDemand/pull/177) + * Notifications in callback … it would make sense to have a specific OAS for notifications to ease the generation of endpoints for the api consumer + * (Update: Robert and Patrice created an issue for that in Commonalities: https://github.com/camaraproject/Commonalities/issues/8) +* Discussion of the linting PR + * Timing -> v0.10.0 + * Herbert will check alignment with issue in commonalities + * Herbert has the necessary admin rights to deploy +* Scope of v0.10.0 … input from Open Gateway Product team - presentation by Jorge + * Brief introduction of the new WoW being define between GSMA and CAMARA, to provide requirements coming from GSMA Product stream into CAMARA. + + +## AOB + +* Topics for next call + * Creation of Release v0.9.0? +* The next call will be on July 14th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..322b85eb35eba3762b9f0eaa608bb04c6eab1700 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14/raw.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - MOM-2023-07-14 + +*July 14th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Agenda + +* Open Issues +* Open PRs +* API Roadmap +* AOB + + +## Open Issues + +* [#174 Simplify Event Model for Notification in v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/174) + PR #177 is open, will get closed with it + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + PR #171 open for this, will be address after release of v0.9.0 + +* Other issues not discussed + +## Open PRs + +* [#177 fix(openapi): Add inheritance beetween Event and QosStatusChangedEvent](https://github.com/camaraproject/QualityOnDemand/pull/177) + Jose will revert towards the current NotificationEvent structure as defined in Design Guidelines (as proposed in https://github.com/camaraproject/QualityOnDemand/pull/177#issuecomment-1635517840) + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Will be addressed after release v0.9.0 is done. To be decided which linters will be activited at the start. Alignment with rule set which is in work at Commonalities tbd. + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + Not discussed, will be part of v0.10.0 + + +## API Roadmap + +### Release 0.9.0 + +* Release 0.9.0 ready to be released after merge of PR #177 +* Herbert will create respective issue and PR next week +* Randy reported that his team has successfully implemented the releace candidate and didn't encountered new issues + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and potentially from Notifiation/Subscription in Commonalities + * Current guideline not optimized for implicit notification subscription as in QoD API +* New features to be discussed in next call + * e.g. PATCH operation + +## AOB + +* The next call will be on July 28th, 2 PM CEST / 12:00 UTC +* Proposal to skip the call on August 11th (summer break) diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..40d049dfbc0a017ff6e13162103e9ec3c0dbffa1 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28/raw.md @@ -0,0 +1,109 @@ +# Camara QoD meeting - MOM-2023-07-28 + +*July 28th, 2023* + +## Attendees (not complete - add if needed) + +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + + +## Sub Project Management + +* Release v0.9.0 done +* Patrice Conil and Randy Levensalor added as additional maintainer of QoD Sub Project +* Shilpa Padgaonkar stepped back as code owner, Eric Murray and Randy Levaensalor added as codeowners +* Next meeting on August 11th: Eric will take the moderation + + +## Open Issues (including backlog) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) +To be replaced by an issue to adapt to changes out of #8 in Commonalities + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +Most potential customers are ok with a fallback to "default" class of QoS. Notion that implementation would be complex (at the moment) but limited market demand. To be kept in backlog. + + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) +PR #162 open. Agreed to implement first a minimum patch operation as described in comments. Behaviour behind patch of `duration` to be discussed first within the issue. Potentially an own endpoint necessary if the behaviour doesn't fit to a PATCH operation. + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +Syed mentioned the need to describe flows also with the protocol type (TCP, UDP). Use case examples to be added as comments. Might not require the introduction of IPFlowDescriptions. Decision if to pull from backlog based later. + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) +Nice to have functionality for developers. Requires to maintain relation of QoD session resources to resource owner based (based on access token). Should if possible get part of v0.10.0. therefore backlog label deleted. + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) +Two options seen in discussion: + * Use of comparisation operators on attributes. For that a definition in Commonalities (how to express in OAS) is pending. Challenge: need to be applied to complex object + * Additional GET endpoint which delivers based on a profile object with required/desired parameters a list of QoD profiles which are fulfilling the required quality parameters (if existing). This would require a specific comparisation logic. GraphQL could be a blueprint, but QoD sub project should introduce that only if there is broader demand across CAMARA sub project. Discussion to be continued within issue.

                          + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + PR #171 open for this, Randy will break it down into smaller PRs in order to introduce linting in steps. + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) +Missed to discuss => next call + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +See comments within issue. Probably no change to the API, only relevant for implementation of certain profiles. Discussion to be continued within the issue. + + +* [#192 Change version number in main to v0.10.0-wip](https://github.com/camaraproject/QualityOnDemand/issues/192) Herbert will do a short PR with this change + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) Discussion points (to be continues within the issue): + * Main use would be to relate usage data from the network to a specific application of the API customer. Relevant for API customers who have different applications or application functions which they want to monitor regarding usage seperately. Assumption is that the application information will not come with the access token (as that would require different access token per application). + * This functionality (add application ID to the API call) might be relevant across several CAMARA APIs -> potentially issue to be opened in Commonalities. + +## Open PRs + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Randy will split the PR into several smaller PRs to introduce linting step by step + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + See discussion of issue #47 (update: changed status of PR to "draft" as we first want to discuss the logic behind patching `duration`) + + +## API Roadmap + +### Release 0.9.0 + +* Release 0.9.0 is done +* Prover implementations (PI) need to be updated, Herbert to create issues within the repositories + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notifiation/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) (minimal set of attributes which can be patched) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + + +## AOB + +* QoD maintainers are reqquested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on August 11th, 2 PM CEST / 12:00 UTC + * Herbert on vacation, Eric will moderate + diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a8ec0a65e8fa38064ca318aafd526ffc0950292b --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11/raw.md @@ -0,0 +1,133 @@ +# Camara QoD meeting - MOM-2023-08-11 + +*August 11th, 2023* + +## Attendees + +* Eric Murray (Vodafone) +* Thorsten Lohmar (Ericsson) +* Patrice Conil (Orange) +* Emil Zhang (Ericsson) +* Randy Levensalor (CableLabs) +* Toshiyasu Wakayama (KDDI) +* Syed A Rehman (Verizon) +* Jose Luis Urien Pinedo (Telefonica) +* Akos Hunyadi (Deutsche Telekom) +* Rafal Artych (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Bhabani Panda (Meta) +* Vidhi Mehta (Comviva) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* Release v0.9.0 done +* Next meeting on August 25th + +## Open Issues (including backlog) + +### Issues discussed during meeting + +* [#199 QoD 0.9 - inline documentation problem](https://github.com/camaraproject/QualityOnDemand/issues/199) +
                          Proposal to include link to Swagger editor or ReDoc formatted version of the API specification within the release notes + - General agreement that this was a good idea + - **Decisions:** + - Add inline links to Swagger and Redoc formatted version of API definition to both release notes and README.md (for latest release) + - Raise with Commonalties to make this a requirement for all APIs + - Eric to request Herbert update release notes and README for QoD + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) +
                          Automatic linting of API specification before being merged into repository + - **Decisions:** + - Agreed that this was a good time to test linting on v0.10.0-wip before this is further modified + - Randy to look to implement this first for simple formatting update (prettifying) to understand how linting tools can be applied to the repository. If insufficient permissions for this, Randy will contact Herbert. + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) +
                          Main use would be to relate usage data from the network to a specific application of the API customer. Relevant for API customers who have different applications or application functions which they want to monitor regarding usage separately. Assumption is that the application information will not come with the access token (as that would require different access token per application). + - Syed gave a [presentation](https://github.com/camaraproject/QualityOnDemand/blob/6d6cca9162f491db6b5ff501d1bce80ece0ab900/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx) on this issue. The following clarifications and comments were made: + - Relationship between API consumer Id, application server IP address, and proposed appId is not necessarily one-to-one + - API consumer may be managing multiple application servers + - Application servers may have more than one IP address, or share a single IP address with multiple applications + - An alternative to explicitly identifying the application by appId would be for each application to be identified by a separate OAuth key / token + - For some API consumers, however, this could be unmanageable + - This solution would also be effectively proprietary, requiring the OAuth key identity to be extracted and passed to the API using, for example, a header + - If an explicit appId was passed via the API, validating this would be an issue + - Some workflow examples of appId validation and error cases would be useful + - For mobile networks, appId would map to aspId (or sponsorId) of NEF. There is no equivalent mapping for fixed networks, so use of appId would likely be proprietary. + - Accessing records by appId would remain proprietary for each API implementor, with no plans to introduce additional CAMARA APIs for this + - This functionality (add application ID to the API call) might be relevant across several CAMARA APIs -> potentially issue to be opened in Commonalities. + - **Decisions:** + - Syed to make proposal on how appId would be introduced into the QoD API definition, and to give additional details on how it would be validated and used. + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) +
                          Previous discussion of options: + - Use of comparison operators on attributes. For that a definition in Commonalities (how to express in OAS) is pending. Challenge: need to be applied to complex object + - Additional GET endpoint which delivers based on a profile object with required/desired parameters a list of QoD profiles which are fulfilling the required quality parameters (if existing). This would require a specific comparison logic. GraphQL could be a blueprint, but QoD sub project should introduce that only if there is broader demand across CAMARA sub project. Discussion to be continued within issue. + +
                          Issue was further discussed during meeting: + - Probably only required if the number of QoS profiles is large + - For mobile networks, this is unlikely given the difficulties radio networks have in balancing multiple different QoS requirements + - For fixed networks, it is more likely that the number of offered profiles will eventually be large, but not for initial deployments of the API + - Exact requirements still not clear + - Do we need ranges, or just greater than (or equal) or less than (or equal) to specified value? + - API definition support for filtering by ranges / inequalities is currently being discussed in [Issue #10](https://github.com/camaraproject/Commonalities/issues/10) in Commonalities. + - **Decisions:** + - Probably not required for v0.10.0. Randy to consider when this might be required. + - Randy to formalise requirements so that they can be fed into Commonalities and taken into account in any modified filtering scheme + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - Randy proposed that DSCP be an explicit parameter of a QoS profile. Probably a single parameter applying to both upstream and downstream traffic. + - Not clear how this parameter would apply to mobile network. Mobile network operators / equipment vendors input welcome. + - Parameter could not be enforced outside of CSP's won network + - **Decisions:** + - Randy to make proposal to add DSCP as an explicit but optional parameter of the QoS profile + - Mobile network operators / equipment vendors to comment in the issue of the value of this for mobile networks + +### Issues not discussed during meeting + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs - Not directly discussed during meeting + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Randy will split the PR into several smaller PRs to introduce linting step by step + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + See discussion of issue #47 (update: changed status of PR to "draft" as we first want to discuss the logic behind patching `duration`) + + +## API Roadmap + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) (minimal set of attributes which can be patched) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Probably excluded from next release + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + + +## AOB + +* QoD maintainers are requested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on August 25th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..501d85781d7f858348d7ad7078b73289c3df06aa --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25/raw.md @@ -0,0 +1,106 @@ +# Camara QoD meeting - MOM-2023-08-25 + +*August 25th, 2023* + +## Attendees (not complete) + +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* no updates + +## Open Issues (including backlog) + +### Issues discussed during meeting + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) +
                          Automatic linting of API specification before being merged into repository + - Randy added as a codewoner, will allow him to merge respective PRs + - Stepwise approach + - Swagger editor validator (PR #206) merged during the call + - Megalinter (PR #215) as netx step + - DT will take of JAVA linting + + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - Presentation update uploaded: https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx + - Jose: close relation with identity discussions within Identity&Consent and GSMA + - Syed to provide a proposal as a PR + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - Most probably only few profile within mobile networks, probably more in fixed networks upcoming + - Decision: not in scope for v0.10.0, we will wait until a larger number of profiles are in use + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - no update, discussion to be continued in the issue + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - depending on authentication/identity of API consumer + - DT considers to make a proposal + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - Discussion + - Change of session duratin should be done with an explicit endpoint which will allow to include the necessary logic behind. "Patching" the duration would be unclear regarding impacts. + - Patching notificationAuthToken: to be reconsidered after new notification/event approach is concluded in Commonalities (including security concept) + - Decision + - PR for new endpoint to change session duratin (Emil) + - no further PATCH operation as of now + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - waits for general solution in Commonalities. + - request to participate in the discussion there (especially https://github.com/camaraproject/Commonalities/pull/56) + + +### Issues not discussed during meeting (backlog items) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs + +* not directly discussed within the meeting + +## API Roadmap + +### Release 0.10.0 (only updated) + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47 (will be realized as new endpoint for change of session duration, no PATCH operation for a session) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Excluded from next release + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) => changed back to backlog item + + +## AOB + +* QoD maintainers are requested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on September 8th, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..df60ba24be25882149b3dc714d92d301facc3334 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08/raw.md @@ -0,0 +1,115 @@ +# Camara QoD meeting - MOM-2023-09-08 + +*September 8th, 2023* + +## Attendees (potentially not complete) + +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Jason Mei (Whale Cloud) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Ludovic Robert (Orange) +* Thorsten Lohmar (Ericsson) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* From TSC (Herbert, Eric): + * TSC participants and all active maintainers are asked to review and comment on the currently open issues and PR for event and notification structure in Commonaltities - especially issue pull request [Update DG with use of callbacks & cloudEvents #56](https://github.com/camaraproject/Commonalities/pull/56). The PR need to be closed soon and has to adapted by the sub project + * For other points from TSC see minutes of TSC which will be added to https://github.com/camaraproject/Governance/tree/main/documentation/MeetingMinutes/TSC + +* Introduction of linting (was issue #158) + * Linting of YAML file was introduced with PR [Megalinter initial #207](https://github.com/camaraproject/QualityOnDemand/pull/207). The PR contains also the (minor) changes within qod-api.yaml to adapt to linting. Beside correction of spaces one example needed to be corrected and URL variables to be replaced with concrete examples. + * During last two weeks two small changes to Megalinter configuration + * PR #215 will enable in addition the linting of Java files + + +## Discussion of Open Issues + +### Issues discussed during meeting + +* [#209 Add 400 - Bad Request for an invalid sessionId GET + DELETE /sessions/{sessionId}](https://github.com/camaraproject/QualityOnDemand/issues/209) + * PR ready to be merged, adding generic 400 for the two endpoints + * The change will go into v0.10.0, patch for v0.9.1 only if someone their is demand for that + +* [#204 Move the "description" out of "allOf"-declaration](https://github.com/camaraproject/QualityOnDemand/issues/204) + * PR #205 ready for final review + * Swagger editor and redoc are still showing the right descriptions with the proposed approach; "allOf" declaration as workaround still needed even with only one element (otherwise the generic description of the referenced schema will be shown) + * AP Randy to do a final check with his development team before approval + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) and updated presentation in https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx + - [PR #217](https://github.com/camaraproject/QualityOnDemand/pull/217) provided by Syed, first comment from Eric available + - Issue and PR open for discussion, labels added accordingly + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - Discussion of the latest comments on the issue + - AP Randy to summarize the results of the discussion within the issue itself + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * Already closed, see above in "Sub Project Management" + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - moved into backlog, excluded from v0.10.0 scope + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - no update + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - To be replaced with new issue which fits to Emil’s PR + - AP Herbert: create issue and relink the PR + - PR [#216 Extend or reduce session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) opened as a proposal + - Discussion if the operation should allow also to reduce the session duration or only extend it ... some voices to allow only extend. For reduction of session duration there should be an use case presented, which justifies the effort to implement the logic (especially if the resulting duration is less then the already elapsed duration) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - waits for general solution in Commonalities + - request to participate in the discussion there (especially https://github.com/camaraproject/Commonalities/pull/56) + + +### Issues not discussed during meeting (backlog items) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs + +* all open PRs are already mentioned above + +## API Roadmap + +### Release 0.10.0 (only updated) + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) - will be realized as new endpoint for change of session duration, no PATCH operation for a session planned anymore + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Excluded from next release + * Backlog Issues: #166, #147 (see last MoMs), #51, #45 + * Note: #31 (Ensure secure handling of callback URL will be addressed by new notification structure) + +## AOB + +* The next call will be on September 22nd, 2 PM CEST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c0da611a53a96796e6857061969f0ac98268df14 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22/raw.md @@ -0,0 +1,97 @@ +# Camara QoD meeting - MOM-2023-09-22 + +*Friday, September 22nd, 2023* + +## Attendees + +* Eric Murray (Vodafone, Moderator) +* Rafal Artych (Deutsche Telekom) +* Patrice Conil (Orange) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Emil Zhang (Ericsson) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Submitted as a replacement for [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162), which is now closed + * Based on feedback received, scope is limited to extending session durations only. PR remaned. + * Two discussion points remain open with the PR: + * New endpoint requires an associated security scheme (now agreed) + * Should extending session durations beyond the maximum allowed for a new session (currently 1 day) be allowed? + * **If participants have a view on whether sessions can be extended beyond 1 day maximum duration, please comment in the associated issue** + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Two discussion points currently open + * Exact relationship between `applicationConsumerId` and the end user, API consumer and other actors in the API transaction is not clear. In particular, for three-legged authentication, should the `applicationConsumerId` be provided at the authorisation stage (in the same way as, for example, `phoneNumber`)? + * Should `applicationConsumerId` be a "top level" parameter in the `CreateSession` schema, or part of the `ApplicationServer` schema? + * **Syed to clarify exact scope of `applicationConsumerId`, and maybe consider renaming** + * **Participants with a view on either open point, or with additional open points, to comment in the associated issue before the next meeting** + +## Discussion of Open Issues + +### Issues For Next Release + +* [#221 Change event structure and notification according to Design Guidelines changes](https://github.com/camaraproject/QualityOnDemand/issues/221) + * A revised model for callbacks is close to being agreed within Commonalties (see Commonalities [#56](https://github.com/camaraproject/Commonalities/pull/56)) + * The revised model must be adopted by QoD for release 0.10.0 + * **Jose Luis volunteers to prepare the necessary PR** + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * Still not clear if the proposed new parameter is relevant for mobile networks + * Waiting for Randy to summarize the results of the discussion and make a specific proposal for required API changes and their impact on API behaviour + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - Akos to update issue with DT's current view on this proposal now that they have feedback from developers + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - Use case of refreshing OAuth token for callbacks remains open + - Jose to review new approach to callbacks being defined by Commonalities to see if this issue is covered there. If not, this requirement can continue to be discussed within the issue. + +* [#209 Add 400 - Bad Request for an invalid sessionId GET + DELETE /sessions/{sessionId}](https://github.com/camaraproject/QualityOnDemand/issues/209) + * Closed by PR [#210](https://github.com/camaraproject/QualityOnDemand/pull/210) + +* [#204 Move the "description" out of "allOf"-declaration](https://github.com/camaraproject/QualityOnDemand/issues/204) + * Closed by PR [#205](https://github.com/camaraproject/QualityOnDemand/pull/205) + +### Backlog Issues + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + - Stale issue + - Akos to check on status within DT and whether this is still required + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - No updates on this issue + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + - No requirement for this capability yet identified + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + - No update on this issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - To be reviewed when new callback approach is adopted. To remain open for now. + + +## API Roadmap + +### Release 0.10.0 + +* Not discussed + +## AOB + +* The next call will be on Friday October 6th, 14:00 CEST / 13:00 BST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4a10faba89cbc250957768177770a3e434630e84 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06/raw.md @@ -0,0 +1,112 @@ +# Camara QoD meeting - MOM-2023-10-06 + +*Friday, October 6th, 2023* + +## Attendees + +* Herbert Damker (Deutsche Telekom, Moderator) +* Eric Murray (Vodafone) +* Rafal Artych (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) +* George Haddad (Liberty Global) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Housekeeping +* Release 0.10.0 +* Open PRs +* Open Issues +* AOB + + +## Housekeeping + +* Next call on Oct 20th collides with OGW f2f meeting in London. Decided to keep the call. + +## API Roadmap + +### Release 0.10.0 + +* Focus of the release v0.10.0 is to adapt to the current changes within Commonalities +* Enhancement which are ready will be taken into the release, but we don't wait for them. They can go into a following release. +* Background is that some operators (e.g. DT) need to decide which version to implement for customers. v0.9.0 would require breaking changes shortly afterwards to get compliant to Commonalities (e.g. event and notification structure) +* If possible: PRs for v0.10.0 ready until next call (Oct 20th), RC ready in the call afterwards (Nov 3rd) + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Open discussion point from previous meeting: + * Should extending session durations beyond the maximum allowed for a new session (currently 1 day) be allowed? + * Discussion result: + * New remaining session duration should not exceed the 1 day maximum duration (remaining duration + extension <= 86400 seconds) + * If new remaining session duration would exceed 86400 seconds, no error should be raised but session duration set to value where the remaining session duration is about 86400 seconds + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Two discussion points are still open + * Naming of the identifier should be changed to express the relationship to API consumer (identity within access token). According to Syed the main purpose is to allow the API consumer to track the API and resource usage more granular then on level of API consumer identity only. An API consumer could have different application functions which they might want to see differentiated on a bill. "applicationConsumerId" is misleading here. + * If the Id is related (one to one?) to an application (server) it would make sense to move it into the applicationServer object. But that might be specific to QoD API and not apply to other APIs. The enhancement should be discussed within Commonalities first. + * **Syed to clarify exact scope of `applicationConsumerId`, and maybe consider renaming. Also to clarify the expecation of (usage) data collected related to the Id by the network (to allow estimation of implementation effort)** + * **Syed to address and drive the topic in Commonalities as it might be relevant for further APIs, not only QoD** + * **Participants with a view on either open point, or with additional open points, to comment in the associated issue before the next meeting** + +## Discussion of Open Issues + +### New Issue since last meeting + +* [#223 Operation tags in global tags element](https://github.com/camaraproject/QualityOnDemand/issues/223) + * Tags are relevant to sort operations e.g. within swagger editor (see [View it on Swagger Editor](https://editor.swagger.io/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/release-0.9.0/code/API_definitions/qod-api.yaml)) + * **Rafal to propose necessary change to fulfill the linting rule as a PR** + +### Issues For Next Release + +* [#221 Change event structure and notification according to Design Guidelines changes](https://github.com/camaraproject/QualityOnDemand/issues/221) + * A revised model for callbacks is agreed and merged within Commonalties (see Commonalities [#56](https://github.com/camaraproject/Commonalities/pull/56)) + * The revised model must be adopted by QoD for release 0.10.0 + * **Jose Luis volunteers to prepare the necessary PR (update after call: [PR #224](https://github.com/camaraproject/QualityOnDemand/pull/224) available for review)** + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * No update, waiting for Randy to summarize the results of the discussion and make a specific proposal for required API changes and their impact on API behaviour + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - DT team is working on a proposal, Akos will provide a PR when ready (might not make it into v0.10.0) + - Jose has commented in the issue. TEL is working on a proposal, e.g. elaborating the requirements around which sessions are allowed to be discovered by certain client, which filters may apply to that query, e.g. searching for sessions for certain MSISDN + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - No update, previous comments still valid + - Use case of refreshing OAuth token for callbacks remains open + - Jose to review new approach to callbacks being defined by Commonalities to see if this issue is covered there. If not, this requirement can continue to be discussed within the issue. + + +### Backlog Issues (only partly discussed) + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + - Stale issue + - Herbert: it isn't a DT issue or requirement, it was originally brought up by Ericsson and just reported by DT. + - There are no requirements for this capability yet identified + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - No updates on this issue + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + - No requirement for this capability yet identified + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + - No update on this issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - To be reviewed when new callback approach is adopted. To remain open for now. + + + +## AOB + +* Note: Next call will collide with OGW F2F meeting in London, some participants might be not available +* The next call will be on Friday October 20th, 14:00 CEST / 13:00 BST / 12:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..990b062b9a5b9f996302e0195aad6f890218a06d --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03/raw.md @@ -0,0 +1,83 @@ +# Camara QoD meeting - MOM-2023-11-03 + +*Friday, November 3rd, 2023* + +## Attendees + +* Herbert Damker (Deutsche Telekom, Moderator) +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Rafal Artych (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) +* Ramesh Shanmugasundaram (Spry Fox Networks) + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Release v0.10.0 +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Ready for final review => Action point for all to review and approve or comment + * Please have a specific view on the description, if it is understandable + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * It is still open when and how the `applicationId` will be agreed between API client and API provider but there is common understanding that this need to be an agreed identifier + * According to Syed this has to happen within an application onboarding process between the operator and the application service provider + * With that there is a relation to the Onboarding Playbook under discussion within GSMA Open Gateway business stream and especially with the "Operate APIs" currently in design phase within TM Forum to support the onboarding process in case of an aggregator between application service provider and operator + * It is also possible that the application will be identified within the authorization token coming with the API call, e.g. if different client IDs are used per onboarded application + * The above points need to be clarified before we add the identifier to the API parameters + * Syed will get in contact with the colleagues within the Operate API working group in TMF, Jose will provide contacts + * Decision: + * The requirement to have an identifier which allows to track the usage per application will be kept + * The PR will be set into draft status until the above questions are clarified + +[#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) - Issue 221 + * The PR should reflect the latest definitions within CAMARA Design Guidelines, ready for final review + * Jose proposed to add Ludovic Robert as reviewer (done) + * Request to all to review asap + +[#227 Adding global tags element](https://github.com/camaraproject/QualityOnDemand/pull/227) + * Decision to use "Title Case" for all tags for now and adapt potentially later if Commonalities decides differently (open issue [#80](https://github.com/camaraproject/Commonalities/issues/80)) + * With this change the PR will be ready for review + +[#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) - Issue #101 + * PR still in draft, but should be - if possible - be part of v0.10.0 + * Decision about which sessions to be returned back to the API client: for now we define it generic/abstract as "all sessions the presented authorization token has (read) access to". That allows to define further details if there are changes within the authorization flow + * Request to make the PR ready for final review + +## New Issues + +* [#230 Single IPv6 addresses within device]() + * New issue from Jose + * IPv6 address most probaly can not covered correctly by a regex + * Note: At least for some mobile networks (e.g. DT Germany) already the prefix is related to an unique and will be match to identify the device + +All other open issues either in work (see above) or not considered for v0.10.0 and therefore not discussed due of time. + +### Release 0.10.0 + +* Release candidate v0.10.0 to be created after the above discussed PRs are reviewed and merged: + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) + * [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) +* Target is to get these PRs reviewed and merged until next call on Nov 17th, so that we can decide the release candidate there +* Release candidate will be the starting point for implementations. Release to be expected about 2 or 4 weeks later. +* Herbert will create the issue with this release plan + +## AOB + +* The next call will be on Friday November 17th, 14:00 CET / 13:00 BT / 13:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6fc88790d7fccc3857e990c70d459e204725c348 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17/raw.md @@ -0,0 +1,100 @@ +# Camara QoD meeting - MOM-2023-11-17 + +*Friday, November 17th, 2023* + +## Attendees (probably incomplete) + +* Andrew Wajs (Scenera) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Discussed Issues +* Release v0.10.0 +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Tag of operation updated (belongs to `QoS Sessions`) + * Description updated + * ACTION ITEM - final review by code owners for approval until Wed Nov 22nd + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * PR in draft status, not discussed + +[#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) - Issue 221 + * Data object optional within Event base class (in line with other APIs using CloudEvents). Can be adapted if there is a global change within guidelines + * ACTION ITEM - final review by code owners for approval until Wed Nov 22nd + +[#227 Adding global tags element](https://github.com/camaraproject/QualityOnDemand/pull/227) + * PR is merged and issue closed + +[#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) - Issue #101 + * PR still in draft, and it is unclear if the open points can be resolved in time for v0.10.0 (see below ... release candidate should be created end of next week which require to have the PR ready for review start of the week) + * Still optional for v0.10.0. + * Discussions: + 1. Can the endpoint deliver (A) all sessions created by the requesting API consumer or (B) only the ones for the user resource within the (3-legged) token? (in other word: does the endpoint later require 2-legged or 3-legged token, in case 3-legged token will (later) be required to create a QoD session resource) + * For now the assumption is that the operation delivers all sessions which are authorized by the token (all sessions created for 2-legged, only user sessions for 3-legged). Decision about needed token is postponed. + 2. Should the operation deliver the full session information or just the session ids? + * Result of the discussion: return the full session information + * Rational: this is the more developer friendly option, as otherwise the API consumer would need to call getSession one by one to find the information they are looking for. From privacy perspective has the API consumer provided and seen all personal information already during the respective session creations. It should be enough that the API consumer was authorized to create the sessionId(s) to assume consent for the get operation. + 3. Is paging needed or not? + * That depends on the answer to point 1. If only the sessions for one user device are delivered is no paging necessary. If all sessions for an API consumer are delivered then paging might be needed to avoid excessive data within the response + 4. Filtering by `device` or `phoneNumber` (Added after the call, comment from Randy https://github.com/camaraproject/QualityOnDemand/pull/228#discussion_r1397522143) + * Potentially the discussions can be not be closed for v0.10.0, in this case the feature will be postponed to the next release. + +[#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) + * PR creates the directory `Test_definitions` and copies the existing .feature file into this directory. + * The question what should happen with the JAVA code within the /cucumber folder can not be answered within the context of the PR + * It is about the general questions if such code (to execute the test definitions) could be provided centrally for all APIs, and if yes, where (e.g. in Commonalities or Release Management) + * ACTION ITEM: Rafal to create an issue in Commonalities for an initial clarification + * The PR itself is ready for final review by code owners (and does not change the API definition). Will go into v0.10.0 + + + +## Discussed Issues + +* [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) + * Agreed to follow the proposal within Jose's comment https://github.com/camaraproject/QualityOnDemand/issues/230#issuecomment-1812335931 - only formats allowed in device would be those considered in [JSON-schema](https://json-schema.org/understanding-json-schema/reference/string#ip-addresses) (`ipv4` and `ipv6`). + * `devicePorts` might need be (re)defined later. + * ACTION ITEM: Jose to create a PR asap, so that it can potentially go into v0.10.0 + +[#231 Error behaviour when session cannot be created due to "time cap" limitation](https://github.com/camaraproject/QualityOnDemand/discussions/231) + * Opened as discussion, not as an issue - hasn't received any attention as a discussion + * The question is actually not QoD specific, but relevant for all APIs (as there could be a cap of agreed number of API calls or a lack of prepaid money) + * ACTION ITEM: Jose to create issue in commonalities + + +All other open issues either in work (see above) or not considered for v0.10.0 and therefore not discussed due of time. + +## Release plan for 0.10.0 + +* **The release candidate for v0.10.0 should be created at end of next week (Friday Nov 23rd) to have enough time to validate the release candidate by implementing operators and do the actual release of v0.10.0 at latest before year end break.** +* The following PRs MUST be included in the release candidate v0.10.0 + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) + * [#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) +* The following PRs COULD be included within the release candidate if finalized in time + * [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) + * Yet to be done PR for issue [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) +* Release candidate will be the starting point for implementations. Release to be expected about 2 or 4 weeks later. +* Between release candidate and release only bug fixes and updates of documentation will be done on the API spec. +* ACTION ITEM: Herbert will create the issue with this release plan and prepare the changes to CHANGELOG.md + +## AOB + +* The next call will be on Friday December 1st, 14:00 CET / 13:00 BT / 13:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..22b5c383590b1d27abcf88b1bfd712c3277dcc8c --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01/raw.md @@ -0,0 +1,115 @@ +# Camara QoD meeting - MOM-2023-12-01 + +*Friday, December 1st, 2023* + +## Attendees (probably incomplete) + +* Akos Hunyadi (Deutsche Telekom) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Jan Frimann (Ericsson) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Merged PRs & Release Candidate v0.10.0 +* Discussed Issues +* AOB + +## Merged PRs & Release Candidate v0.10.0-rc + +* The following PR were merged since the last meeting: + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) after final review + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) after final review + * [#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) + * [#237 Single IP addresses in Device model specified with standard formats instead of patterns](https://github.com/camaraproject/QualityOnDemand/pull/237) + * PR was create to address [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) + * Jose explained the motivation, discussion and consequences of the PR + * Within `device` object only single IP addresses (IPv4 or IPv6) will be used to identify a device, the respective json formats are used to define the parameter type + * The change has only an impact for API consumers which used an IPv6 address range to identify a device (this is mentioned within the CHANGELOG.md for v0.10.0-rc) + * The schema in `applicationServer` are renamed and the restrictions of the format with regex are eliminated + * For API consumers these changes have no impact + * The PR was merged + +* PR [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) + * was set back to draft, due to the fact that the discussions within the issue couldn't be concluded in time and if, would have required larger changes within the PR + * the issue and PR are postponed to the next release after v0.10.0 + +* PR [238 Creation of release candicate v0.10.0-rc](https://github.com/camaraproject/QualityOnDemand/pull/236) + * Herbert presented the PR with the updates of CHANGELOG.md, README.md and the change of version number within the YAML file to v0.10.0-rc + * The PR had already four approvals and was merged live during the meeting + * Herbert created the Github release with the tag v0.10.0-rc and the release branch release-0.10.0 + * With that the release candidate is available and all interested parties are asked to start implementation and report bugs they encounter during the implementation + * The actual release will happen most probably in January + +* Jan asked to move the user friendly links with swagger editor and redoc as first items and "hide" the link to the pure YAML file behind + * AP: Herbert will open an issue for that + + +## Discussion of Open Issues + +* [#238 Remove mobile from QoD scope](https://github.com/camaraproject/QualityOnDemand/issues/238) + * New issue created by Randy to get the scope of QoD API more inclusive beyond mobile networks + * Question if the scope is then aligned with HomeDevicesQoD or if there is an overlap + * This need to be checked and based on the result the scope can be reformulated + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Issue and related PR currently on hold until it is clarified which information about the application will be already be already part of the autorization token and can be derived from there + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * No update + * Could most probably be one option to define flows (see below) + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * Potential candidate for v0.11.0 + * Adding another endpoint with `device` parameter in body of POST operation could be one option + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * Active discussion, priority candidate for v0.11.0 + * phoneNumber not allowed within query parameter => operation has to be changed to POST, with body for filter parameters + * this change will allow then to use complete `device` object to be added for filtering + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + * Issue to be replaced with new issue to rework the flow definition parameters in general (devicePort, applicationServerPort) and potentially add further options, e.g. DSCP markings (see #173) + * Action Point: create new issue, close #51 + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + * "Extend duration" addressed the identified paramter for a "patch" + * Issue to be closed, new issues to be opened if other attributes of a session are to be updated + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + * Backlog item, currently no use case + * Might be part of upcoming QoS profiles + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + * Call back definition are now following the CAMARA design guidelines + * Issue can most probably be closed, to be confirmed + + +## Candidate for v0.11.0 + +* Note: no merging into main for release v0.11.0 until v0.10.0 is finally released + +* Candidates for v0.11.0 (from above discussion) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * New issue for flow definition rework + * will replace #51 + * will have #173 as sub issue + * Update of test definitions (.feature file) + * Discussion and update of security schema for all operations (also prerequisite for #101) + +## AOB + +* The next call will be on Friday December 15th, 14:00 CET / 13:00 GMT / 13:00 UTC diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f228a84fd235b06bc21f71b7be0ba7f76bb3fd55 --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15/raw.md @@ -0,0 +1,111 @@ +# Camara QoD meeting - MOM-2023-12-15 + +*Friday, December 15th, 2023* + +## Attendees (probably incomplete) + +* Akos Hunyadi (Deutsche Telekom) +* Andrew Wajs (Scenera) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Issues relevant for v0.10.0 (RC) +* Issues which are candidates for next release v0.11.0 +* AOB + +## Issues relevant for v0.10.0 (RC) + +* [#239 Bring user friendly links within README into top position](https://github.com/camaraproject/QualityOnDemand/issues/239) + * Fixes with PR #246 (merged during the call) + * Issue closed + +* [#238 Remove mobile from QoD scope](https://github.com/camaraproject/QualityOnDemand/issues/238) + * As long as QoD is about the access line up to the home router there is no overlap with HomeDevices QoD (see [comment](https://github.com/camaraproject/QualityOnDemand/issues/238#issuecomment-1856862249) in issue) + * Randy volunteered to prepare a PR with changes to the documentation (within YAML) and the README.md of the repository (issue assigned to him) + +* [#241 Extend the QoD API documentation with details as to what happens when qosStatus changes from available to unavailable](https://github.com/camaraproject/QualityOnDemand/issues/241) + * Agreed that this issue should be addressed within the documentation, a consistent behavior is across implementations is important + * It's useful that the session resource will exist beyond the time where the qos session became unavailable to allow API consumer who don't use/receive notifications to get the status change and reason (e.g. if polling in regular intervals) + * There will be no case where an "unavailable" QoS session will get "available" again. If we later will define such behavior (that the network tries to reestablish the requested QoS profile) we need to introduce another status (e.g. in context of issue #45, supporting fallback QoS) + * Different options discussed, about how long the session resource should be preserved after the QoS session got unavailable: + * An explicit delete by the API consumer can not be expected in all cases + * Binding to requested duration could be difficult to implement + * Emil proposed to keep the session resource for a fixed time after the session changed to unavailable + * Time to be defined, should cover at least typical polling intervals + * Emil will update his presentation with this proposal + * Design target is to allow developers to decide between notifications and polling, both methods should be sufficient to get all important information + +* [#242 Notifications](https://github.com/camaraproject/QualityOnDemand/discussions/242) + * The discussion topic is suggesting to send notifications for all changes of the status of the QoS Session resources, including the initial entering of "available" and the ones induced by API calls by the API consumer (e.g. delete of the QoS session) + * Discussed that it is important to document in which cases notifications will be send + * As far as possible within the API documentation + * In addition within the test definitions (relevant documentation for implementators) + * Sending a notification in all cases of status change is in line with the above design target, that notifications should be sufficient to get all important information + * Agreement to create an issue out of the discussion, to document the discussed behavior within the API documentation and test definitions + * ACTION POINT - Herbert to create the issue + +## Issues which are candidates for next release v0.11.0 + +These issues have the label "QoD" within https://github.com/camaraproject/QualityOnDemand/issues. +All sub project contributors are asked to add their views to the issues, so that we can start to work on the issues beginning of next year. + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * Left over from v0.10.0 as discussion couldn't be closed, now planned for v0.11.0 + * The discussions have dependencies with #244, see below + * PR #228 on hold (draft) until the discussions are closed + * From last call: + * phoneNumber not allowed within query parameter => operation has to be changed to POST, with body for filter parameters + * this change will allow then to use complete `device` object to be added for filtering + + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * To be defined as new endpoint, POST operation with `device` object in body + * Note: identifying the device via phoneNumber might be not sufficient to return the applicable profiles, e.g. in case a device is served by multiple slices or APNs + * Further discussion within the issue + +* [#243 Rework definition of QoS flow(s)](https://github.com/camaraproject/QualityOnDemand/issues/243) + * New issue as discussed within last meeting + +* [#244 Align securitySchemes and security of QOD API spec with IdentityAndConsentManagement](https://github.com/camaraproject/QualityOnDemand/issues/244) + * New issue for v0.11.0 as discussed in last call + * Herbert proposed an additional issue to "Ensure that the QoD API does not reveal additional PII" beyond the personal information provided by the API consumer. E.g. if the device is identified by IP address, the session information should not in addition contain the phoneNumber and vice versa. Such requirement should be documented within the test definitions. Herbert to create the issue. + +* [#245 Update and enhance test definition file for QOD API](https://github.com/camaraproject/QualityOnDemand/issues/245) + * New issue as discussed within last year + + +The following two issues, labeled as "discussions" are related to the above issues: + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Issue and related PR currently on hold until it is clarified which information about the application will be already be already part of the autorization token and can be derived from there => #244 + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * Could most probably be one option to define flows => #243 + + +## v0.11.0 Release scope & timeline + +Scope of the next release v0.11.0 is described by the issues discussed above + any impacts from releases of Commonalities (v0.10.0 is in line with Commonalities v0.2.0, so any changes coming with further releases of Commonalities) +Time horizon is April/Mai 2024 (definitely after MWC Barcelona). + +## AOB + +* We will skip the call on December 29th +* The next call will be on Friday January 12th, 14:00 CET / 13:00 GMT / 13:00 UTC +* The invites for 2024 will come from the LFX Zoom platform and will be distributed via the mailing list +* For best user experience it is recommended to have an Linux Foundation account, with the same email address behind like for the mailing list subscription. An account can be created on https://openprofile.dev. The account and profile will give also access to the recordings of the meetings and to the wiki.camaraproject.org +* We will use the https://wiki.camaraproject.org for minutes going forward diff --git a/marked/QualityOnDemand/documentation/MeetingMinutes/README/raw.md b/marked/QualityOnDemand/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b422265a8df3662799369f69c86c5b8a357a547c --- /dev/null +++ b/marked/QualityOnDemand/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,5 @@ +## Meeting Minutes of Quality on Demand Sub Project + +Starting with the beginning of 2024 the meeting minutes of Quality on Demand calls are within the CAMARA Wiki at https://lf-camaraproject.atlassian.net/wiki/x/ABje. + +Meeting minutes of 2023 and before are here in the repository. diff --git a/marked/RainfallIntensity/README/raw.md b/marked/RainfallIntensity/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..28f5cc237866a99b4cc15c1f03c9879de84aeec1 --- /dev/null +++ b/marked/RainfallIntensity/README/raw.md @@ -0,0 +1,45 @@ + + + + + + + + + +# RainfallIntensity + +Sandbox API Repository to describe, develop, document, and test the RainfallIntensity Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/DYDEH) + +## Scope + +* Service API(s) “RainfallIntensity” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Obtain the power measurements for the communication links inside a geographical area for a specific time period. The data includes the time of measurement, the transmit and received power, and the link ID (which identifies each link uniquely). + * Obtain the metadata of the communication links within a geographical area. The metadata includes the link ID, time of update, signal frequecny, signal polarization (horizontal or vertical), and location (latetude and longitude) of the transmitter and the receiver. + * Obtain the rainfall data associated with communciation links inside a geographical are for a specific time. The rainfall data include the estimation of rainfall, time stamp, and link ID. +* Describe, develop, document, and test the API(s) +* Started: January 2026 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/AgDHH) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/RainfallIntensity/code/API_definitions/README/raw.md b/marked/RainfallIntensity/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/RainfallIntensity/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/RainfallIntensity/documentation/API_documentation/README/raw.md b/marked/RainfallIntensity/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/RainfallIntensity/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/RainfallIntensity/documentation/SupportingDocuments/README/raw.md b/marked/RainfallIntensity/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/RainfallIntensity/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/RegionDeviceCount/README/raw.md b/marked/RegionDeviceCount/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a788b950c591b68bd1fe6d9a61348e0d217900d0 --- /dev/null +++ b/marked/RegionDeviceCount/README/raw.md @@ -0,0 +1,52 @@ + + + + + + + + + +# RegionDeviceCount + +Sandbox API Repository to describe, develop, document, and test the RegionDeviceCount Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/JSTe) + +## Scope +* Service APIs for “RegionDeviceCount” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points.In addition, this API also provides a filtering function. Customers can filter devices by passing in different constraints. Currently, it supports two filtering conditions: roaming status and device type, and it is designed to be extended in the future + * NOTE: The scope of this API should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/RegionDeviceCount/releases/tag/r2.2) (Fall25), with the following API versions: + * **region-device-count v0.2.0** + [[YAML]](https://github.com/camaraproject/RegionDeviceCount/blob/r2.2/code/API_definitions/region-device-count.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/r2.2/code/API_definitions/region-device-count.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/r2.2/code/API_definitions/region-device-count.yaml) +* The latest public release is always available here: https://github.com/camaraproject/RegionDeviceCount/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/RegionDeviceCount/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/RegionDeviceCount/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly on Fridays 11:00 CET/CEST / 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91734372257?password=28df8c0a-941a-4f41-adc2-fd5de2791a96) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/RegionDeviceCount) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/RegionDeviceCount/code/API_definitions/region-device-count/raw.md b/marked/RegionDeviceCount/code/API_definitions/region-device-count/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7143beec90e25b18108c76574341d5ca57fedab2 --- /dev/null +++ b/marked/RegionDeviceCount/code/API_definitions/region-device-count/raw.md @@ -0,0 +1,754 @@ +# region-device-count + +```yaml +openapi: 3.0.3 +info: + title: Region Device Count + description: >- + Region Device Count API enables API consumers to obtain the number of devices within a certain geographical area during a specific time interval. + + # Introduction + + This API allows for the API Consumer to query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points. + This functionality can be used for multiple use cases, some of the possible use cases for this API are: + + - [Emergency Rescue](https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/main/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md) + + - [Outdoor Live Streaming](https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/main/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md) + + # Relevant terms and definitions + + * **Device Count**: Refers to the total number of devices that appear within a given area and a specific time interval. A device will be counted as long as it appears at least once in the specified area during the time interval. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # API Functionality + + ## Request Parameters and Area Definition + + When making a request, the API consumer needs to specify the area, start time, end time, and filter conditions in the request body. The area can be defined as a circle or a polygon. For a circular area, the center and radius must be provided; for a polygon area, a list of longitude and latitude points must be provided. If the start and end times are not provided, the API will return the current number of devices in the area. + + ## Filter Condition Application + + The filter condition is used for precise device filtering and currently includes two filtering criteria: `roamingStatus` and `deviceType`, with support for future expansion. The `IN` logic is applied for multiple filter items within a single filtering criterion, and the `AND` logic is used between multiple filtering criteria. + + + For example, "filter":{"roamingStatus": ["roaming"],"deviceType": ["human device","IoT device"]}" means the API will only return the number of human network devices and IoT devices in roaming mode. "filter":{"roamingStatus": ["non-roaming"]}" will return the number of all non-roaming devices. Note that at least one filtering criterion must be provided; otherwise, the request will be invalid. + + ## Response Result Explanation + + The API response returns a RegionDeviceCountResponse object containing the device count and status. The status values include `SUPPORTED_AREA` (the entire requested area is supported, and the device count for the entire area is returned, with 100% telecom coverage), `PART_OF_AREA_NOT_SUPPORTED` (part of the area is outside the telecom operator's coverage area, and only the device count within the coverage area is returned, with 50% <= telecom coverage < 100%), `AREA_NOT_SUPPORTED` (the entire requested area has no telecom coverage, and no data is returned, with telecom coverage < 50%), `DENSITY_BELOW_PRIVACY_THRESHOLD` (the number of connected devices in the area is below the local regulatory privacy threshold), and `TIME_INTERVAL_NO_DATA_FOUND` (no device count data is found within the requested time interval). + + ## Callback Function + + The standard behaviour of the API is synchronous, although for large area requests the API may behave asynchronously. An API invoker can enforce asynchronous behaviour by providing a callback URL (`sink`) + is in the request, in this case the API sends a callback to the callback URL provided with the result of the request. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + For requests with a combination of area, startTime and endTime properties involving an amount of processing that cannot be processed synchronously, the API returns the error response REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE. + + For requests with a combination of area, startTime and endTime properties too big for both synchronous and asynchronous processing, the API returns the error response REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST. + + + # Authorization and Authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Region Device Count API does not involve the input and output of user personal data.Therefore, the access to Region Device Count APII is defined as `Client Credentials - 2-legged`. Please refer to [Identify and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/RegionDeviceCount +servers: + - url: '{apiRoot}/region-device-count/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Region Device Count + description: This API allows for the API Consumer to query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points. +paths: + /count: + post: + tags: + - Region Device Count + summary: API operation to get the device count in the specified area during a certain time interval. + description: | + Get the number of devices in the specified area during a certain time interval. + - The query area can be a circle or a polygon composed of longitude and latitude points. + - If the areaType is circle, the circleCenter and circleRadius must be provided; if the area is a polygon, the point list must be provided. + - If starttime and endtime are not passed in,this api should return the current number of devices in the area. + - If the device appears in the specified area at least once during the certain time interval, it should be counted. + + operationId: count + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountRequestBody' + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + required: true + callbacks: + regionDeviceCountCallback: + '{$request.body#/sink}': + post: + tags: + - Region Device Count + summary: 'Region Device Count Callback' + description: | + Important: this endpoint is to be implemented by the API consumer. + The Region Device Count server will call this endpoint when the request result is ready. + operationId: postRegionDeviceCountNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Region device count result. + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountResponse' + examples: + SUPPORTED_AREA: + $ref: "#/components/examples/SUPPORTED_AREA" + PART_OF_AREA_NOT_SUPPORTED: + $ref: "#/components/examples/PART_OF_AREA_NOT_SUPPORTED" + AREA_NOT_SUPPORTED: + $ref: "#/components/examples/AREA_NOT_SUPPORTED" + DENSITY_BELOW_PRIVACY_THRESHOLD: + $ref: "#/components/examples/DENSITY_BELOW_PRIVACY_THRESHOLD" + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + security: + - {} + - notificationsBearerAuth: [] + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountResponse' + examples: + SUPPORTED_AREA: + $ref: "#/components/examples/SUPPORTED_AREA" + PART_OF_AREA_NOT_SUPPORTED: + $ref: "#/components/examples/PART_OF_AREA_NOT_SUPPORTED" + AREA_NOT_SUPPORTED: + $ref: "#/components/examples/AREA_NOT_SUPPORTED" + DENSITY_BELOW_PRIVACY_THRESHOLD: + $ref: "#/components/examples/DENSITY_BELOW_PRIVACY_THRESHOLD" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - region-device-count:count +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for cross-service tracking + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RegionDeviceCountRequestBody: + type: object + description: Payload to get the count of devices in the specific region. + properties: + area: + $ref: "#/components/schemas/Area" + starttime: + type: string + format: date-time + description: Starting timestamp for counting the number of devices in the area. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + endtime: + type: string + format: date-time + description: Ending timestamp for counting the number of devices in the area. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-04T14:27:08.312+02:00" + filter: + $ref: "#/components/schemas/Filter" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + Area: + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + Filter: + description: | + This parameter is used to filter devices. Currently, two filtering criteria are defined, `roamingStatus` and `deviceType`, which can be expanded in the future. `IN` logic is used used for multiple filtering items within a single filtering criterion, `AND` logic is used between multiple filtering criteria. + - If a filtering critera is not provided, it means that there is no need to filter this item. + - At least one of the criteria must be provided,a filter without any criteria is not allowed. + - If no filtering is required, this parameter does not need to be provided. + For example ,`"filter":{"roamingStatus": ["roaming"],"deviceType": ["human device","IoT device"]}` means the API need to return the count of human network devices and IoT devices that are in roaming mode.`"filter":{"roamingStatus": ["non-roaming"]}` means that the API need to return the count of all devices that are not in roaming mode. + type: object + properties: + roamingStatus: + description: Filter whether the device is in roaming mode,'roaming' represents the need to filter devices that are in roaming mode,'non-roaming' represents the need to filter devices that are not roaming. + type: array + items: + type: string + enum: + - 'roaming' + - 'non-roaming' + minItems: 1 + deviceType: + description: Filtering by device type, 'human device' represents the need to filter for human network devices, 'IoT device' represents the need to filter for IoT devices, and 'other' represents the need to filter for other types of devices. + type: array + items: + type: string + enum: + - 'human device' + - 'IoT device' + - 'other' + minItems: 1 + anyOf: + - required: ['roamingStatus'] + - required: ['deviceType'] + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + RegionDeviceCountResponse: + type: object + description: RegionDeviceCount result + properties: + count: + $ref: '#/components/schemas/Count' + status: + $ref: '#/components/schemas/Status' + Count: + description: Device Count + type: number + Status: + description: | + SUPPORTED_AREA: The whole requested area is supported Region Device Count for the entire requested area is returned - Telco Coverage = 100 % + + PART_OF_AREA_NOT_SUPPORTED: Part of the requested area is outside the MNOs coverage area, the area outside the coverage area are not returned - 100% >Telco Coverage >=50% + + AREA_NOT_SUPPORTED: The whole requested area is outside the MNO coverage area No data will be returned- Telco Coverage <50% + + DENSITY_BELOW_PRIVACY_THRESHOLD: The number of connected devices is below privacy threshold of local regulation + + TIME_INTERVAL_NO_DATA_FOUND: Unable to find device count data within the requested time interval + type: string + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - DENSITY_BELOW_PRIVACY_THRESHOLD + - TIME_INTERVAL_NO_DATA_FOUND + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - REGION_DEVICE_COUNT.TIME_INVALID_ARGUMENT + - REGION_DEVICE_COUNT.INVALID_END_DATE + - REGION_DEVICE_COUNT.INVALID_CIRCLE_AREA + - REGION_DEVICE_COUNT.INVALID_POLYGON_AREA + - INVALID_CREDENTIAL + - INVALID_TOKEN + - REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE + - REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument, request body or query param." + GENERIC_400_TIME_INTERVAL_NOT_SATISFIABLE: + value: + status: 400 + code: REGION_DEVICE_COUNT.TIME_INVALID_ARGUMENT + message: "starttime and endtime cannot be passed separately. Either both are passed or neither is passed." + GENERIC_400_INVALID_END_DATE: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_END_DATE + message: "Indicated endTime is earlier than the startTime." + GENERIC_400_INVALID_CIRCLE_AREA: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_CIRCLE_AREA + message: "Missing circle center or radius." + GENERIC_400_INVALID_POLYGON_AREA: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_POLYGON_AREA + message: "The area is not a polygon shape or has an arbitrary complexity." + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 400 + code: REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE + message: "Indicated combination of area or time interval is too big for a sync response" + GENERIC_400_UNSUPPORTED_REQUEST: + value: + status: 400 + code: REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST + message: "Indicated combination of area or time interval is too big" + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic429: + description: Either out of resource quota or reaching rate limiting + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + RETRIEVAL_CIRCLE: + value: + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + starttime: "2023-07-03T14:27:08.312+02:00" + endtime: "2023-07-04T14:27:08.312+02:00" + filter: + roamingStatus: ["roaming"] + deviceType: ["human device", "IoT device"] + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + RETRIEVAL_POLYGON: + value: + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + starttime: "2023-07-03T14:27:08.312+02:00" + endtime: "2023-07-04T14:27:08.312+02:00" + filter: + roamingStatus: ["non-roaming"] + deviceType: ["other"] + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + SUPPORTED_AREA: + value: + count: 100 + status: SUPPORTED_AREA + PART_OF_AREA_NOT_SUPPORTED: + value: + count: 100 + status: PART_OF_AREA_NOT_SUPPORTED + AREA_NOT_SUPPORTED: + value: + status: AREA_NOT_SUPPORTED + DENSITY_BELOW_PRIVACY_THRESHOLD: + value: + status: DENSITY_BELOW_PRIVACY_THRESHOLD +``` diff --git a/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue/raw.md b/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..98ffe7011cae646919ae79372cf94221cc8158c0 --- /dev/null +++ b/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue/raw.md @@ -0,0 +1,10 @@ +# RegionDeviceCount API User Story - Emergency Rescue + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an emergency rescue worker, I hope to be able to obtain the number of users in an area where a special emergency activities could be needed through an API, so as to quickly understand the situation, plan and guide the rescue work..Here is my requirements.
                          •I hope to obtain the number of connected devices on people in the area by providing coordinates or boundary information.
                          •I need the information returned by the API to include the total number and distribution of the devices in that area.
                          •I need to obtain real-time information| +| ***Roles, Actors and Scope*** | **Roles:** API Customer: emergency rescue worker.
                          API Provider:Communication Service Provider (CSP).
                          **Scope:** Returns the real-time number of devices in a specific area through an API | +| ***Pre-conditions*** |The preconditions are listed below:
                          1. The Customer has been onboarded to the CSP's API platform.
                          2. The Customer has successfully subscribed to the RegionDeviceCount product from the product catalog.
                          3. The means to get the access token are known to the API Customer to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** API Customer initiate requests to query the number of devices in a certain area
                            **Ends when:** CSP returns the number of devices in the area to the API Customer. | +| ***Post-conditions*** | CSP returns accurate statistical results, and emergency rescue worker.can quickly locate key rescue areas based on results.| +| ***Exceptions*** | Several exceptions might occur during the RegionDeviceCount API operations
                            - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                            - Invalid input: Not valid input data to invoke operation (e.g.Area format error, or inability to obtain valid data within the area).
                            | diff --git a/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming/raw.md b/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aa0428f3704eadd887ae3fc6a8a0ed0e960478d4 --- /dev/null +++ b/marked/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming/raw.md @@ -0,0 +1,10 @@ +# RegionDeviceCount API User Story - Outdoor Live Streaming + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an outdoor anchor and plan to conduct outdoor live streaming activities in different regions. In order to estimate the possible number of viewers and effectively choose a live streaming location, I need to understand the potential number of viewers in different area.Here is my requirements.
                            • I hope to obtain the number of users in a specific area through an API, so that I can choose locations with high audience potential for live streaming based on this data.
                            • I need an API that can provide information on the activity level of users in the area, in order to determine the activity time of users in that area and arrange the best live broadcast time.
                            • I hope the response time of the API is fast, so that decisions can be made quickly before planning and actual live broadcasts.| +| ***Roles, Actors and Scope*** | **Roles:** End User:Outdoor anchor
                            API Customer: Live Streaming Application.
                            API Provider:Communication Service Provider (CSP).
                            **Scope:** Returns the number of users in a specific area during a certain time interval through an API | +| ***Pre-conditions*** |The preconditions are listed below:
                            1. The Customer has been onboarded to the CSP's API platform.
                            2. The Customer has successfully subscribed to the RegionDeviceCount product from the product catalog.
                            3. The outdoor anchor has been onboarded to the live streaming application.
                            4. The means to get the access token are known to the API Customer to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** Outdoor anchors initiate requests through live streaming application to query the number of devices in a certain area at a certain time interval
                              **Ends when:** CSP returns the number of devices in the area to the live streaming app, and the live streaming app presents the results to the anchors. | +| ***Post-conditions*** | CSP returns accurate statistical results, and users can choose suitable live streaming areas based on the query results | +| ***Exceptions*** | Several exceptions might occur during the RegionDeviceCount API operations
                              - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                              - Invalid input: Not valid input data to invoke operation (e.g.Area format error, or inability to obtain valid data within the area).
                              | diff --git a/marked/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist/raw.md b/marked/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..96f57cb452ea602628dd1b7b249ce25140e67343 --- /dev/null +++ b/marked/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist/raw.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for region-device-count v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                              public | stable
                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/region-device-count.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.2.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/region-device-count.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory1-Emergency_Rescue](/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md) [UserStory2-Outdoor_Live_Streaming](/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/region-device-count.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/region-device-count.feature) | +| 9 | Test result statement | O | O | O | M | N | To be provided | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81134323/RegionDeviceCount+API+description ) | + diff --git a/marked/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10/raw.md b/marked/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ded97bce388e2ac678471d795f62500f081c4905 --- /dev/null +++ b/marked/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10/raw.md @@ -0,0 +1,38 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ludovic Robert (Orange) + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Meeting Schedule Adjust + * Meeting Links are adjusted. Including meeting links. Links of S2C, Region User Count, Network Slice API are split into 3 different meeting links as suggested. + * Meeting times are adjusted. Later the Bi-weekly meeting will start from 5pm CST, 11am CEST. +* Issue#12 Add license file to repository + * Shuting Qing will add the license file. +* Issue#10 User Story 1 - Emergency Rescue,Issue#11 User Story 2 - Outdoor Live Streaming + * Continue the discussion. If there are no other comments, they will be placed in markup format under the documentation folder of the project. +* Issue#9 Support for scenarios when API cannot return a devices count is needed + * Add a status parameter to yaml to identify the query status, with the following enumeration values + * SUBORTED-AREA: The whole request area is supported Population density data for the entire requested area is returned + * Part of the requested area is outside the MNOs coverage area, the cells outside the coverage area are not returned + * AREA-NOT-SUPPORTED: The whole requested area is outside the MNO coverage area No data will be returned + * DENSITY-BELOW-PRIVACY THRESHOLD: The number of connected devices is below privacy threshold of local regulation + * Some specific definitions still need further discussion and clarification +* Issue#8 Support for scenarios when API cannot return a devices count is needed + * The meeting decided to change the API name to RegionDeviceCount to better align with the API intent. Ludovic will help inquire with the working group about the specific process. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, May 24th, 17:00 CST / 11:00 CEST diff --git a/marked/RegionDeviceCount/documentation/MeetingMinutes/README/raw.md b/marked/RegionDeviceCount/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/RegionDeviceCount/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom/raw.md b/marked/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d4d04b73293e6784ff14bdab9fe6e91de0e62550 --- /dev/null +++ b/marked/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom/raw.md @@ -0,0 +1,13 @@ +| **Field** | Description | +| ---- | ----- | +| API family name | Region Device Count | +| API family owner | China Unicom | +| Initial API Contributors | Fan Yang - China Unicom , Jin Xu - Huawei | +| API summary | **Description**
                              This API allows for the API Consumer to query the number of active users (i.e., excluding idle mode users). lin the specified area. The query area can be a circle or a polygon composed of longitude and latitude points.
                              **Use Cases**
                              User Story 1 : Emergency Rescue
                              - As an emergency rescue worker, I hope to be able to obtain the number of users in an area where a special emergency activities could be needed through an API, so as to quickly understand the situation, plan and guide the rescue work.
                              | +| Technical viability | This API is based on real-time location information expansion. It allows obtaining, on a per operator basis, the number of active users in a certain area based on their real-time location. | +| Commercial viability | For use in emergency rescue, disaster relief, intelligent transportation, smart tourism and other scenarios| +| YAML code available? | NO
                              To be provided | +| Validated in lab/productive environments? | YES
                              Available in China UniCom test environment | +| Validated with real customers? | YES
                              For emergency rescue use by the Blue Eye Emergency Rescue Platform | +| Validated with operators? | YES
                              Available for China Unicom in China | +| Supporters in API Backlog Working Group | China Unicom,Huawei | diff --git a/marked/SessionInsights/README/raw.md b/marked/SessionInsights/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c0f54b969b8135735cbb0b275f86db80e7d4cba2 --- /dev/null +++ b/marked/SessionInsights/README/raw.md @@ -0,0 +1,44 @@ + + + + + + + + + +# SessionInsights + +Sandbox API Repository to describe, develop, document, and test the SessionInsights Service API(s) in group with [Connectivity Insights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/93946006/Connectivity+Insights) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/44CaBQ) + +## Scope + +* Concept and Service APIs for “SessionInsights” (see APIBacklog.md) +* The API provides an API Consumer with the ability to: + - report application KPIs to network operator + - receive score from network operator + - receive root cause analysis and recommended corrective actions + - request service improvements +* Note: in first steps the concept will be described with user stories. The relation to existing APIs (e.g. application-profiles, connectivity-insights, quality-on-demand) will be describe to identify if any and which new API(s) are needed +* Describe the concept, develop, document, and test the APIs +* Started: September 2024 +* Originally proposed as Quality by Design (QbD) - has been renamed to SessionInsights to better reflect the scope of the API + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly on Wednesday at 8AM PST (see https://wiki.camaraproject.org/display/CAM/ConnectivityInsights) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vzve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-coi. + * A message to the community of this Sub Project can be sent using sp-coi@lists.camaraproject.org. diff --git a/marked/SessionInsights/code/API_definitions/README/raw.md b/marked/SessionInsights/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/SessionInsights/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/SessionInsights/code/API_definitions/session-insights/raw.md b/marked/SessionInsights/code/API_definitions/session-insights/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..82e2656dc4a1861797b9143c2b0757410ca11061 --- /dev/null +++ b/marked/SessionInsights/code/API_definitions/session-insights/raw.md @@ -0,0 +1,1063 @@ +# session-insights + +```yaml +openapi: 3.0.3 +info: + title: Session Insights + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + description: | + The Session Insights API is part of the CAMARA Connectivity Insights API group. It extends the capabilities of the Connectivity Insights API by enabling applications to continuously monitor and evaluate their real-time session quality, based on observed KPIs and network operator feedback. + + While the Connectivity Insights API allows applications to query whether a network can meet predefined performance thresholds (e.g., jitter, packet loss, bitrate), the Session Insights API supports the lifecycle of an ongoing session. It allows applications to stream KPI metrics to the network operator, receive dynamic scoring on current session performance, and engage in adaptive optimization strategies. + + # Key Features + + - Create a monitoring session using an existing Application Profile. + - Send application-level KPIs (e.g., latency, jitter, throughput, loss) to the network operator. + - Receive a Session Insights Score reflecting network-evaluated session quality. + - Respond to events and adjust application configuration. + - Receive notifications and root cause analysis (RCA) when session quality degrades. + - Request network service improvements using complementary CAMARA APIs (e.g., QualityOnDemand, NetworkAccessManagement). + - Gracefully terminate the session when monitoring is no longer needed. + + # Use of Application Profiles API + + This API leverages CAMARA’s [Application Profiles](https://github.com/camaraproject/ApplicationProfiles) to define threshold criteria for session quality. The Application Profile specifies the application's expected network performance requirements and is referenced when creating a session. + + # Example Use Cases + + ## Wi-Fi Congestion Mitigation + - Application sets thresholds for latency and packet loss. + - Session score drops due to congestion, triggering an RCA event. + - RCA identifies local Wi-Fi congestion; application adjusts QoS policies (e.g., enables WMM) to prioritize traffic. + + ## Access Network Impairment + - Degraded score attributed to poor signal or congestion in the access network. + - Application requests service enhancement through APIs like QualityOnDemand or NetworkAccessManagement. + + # Authorization and Authentication + + ## Identifying the [ device | phone number ](*) from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same [ device | phone number ](*) is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/SessionInsights + +servers: + - url: "{apiRoot}/session-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Session Insights + description: | + Manage the lifecycle of real-time monitoring sessions between an application and the network. + Applications can stream KPIs, receive session scores and event notifications, and take actions + based on current session quality and network conditions. + + +paths: + /sessions: + post: + tags: + - Session Insights + summary: Create a Session Insights session + description: | + Create a new session for monitoring application performance and network + quality. The session can be used to stream KPIs, receive session + scores, and handle RCA events. + + The session is created under an existing Application Profile, which + defines the expected performance thresholds and other parameters. + + The operator allocates a sink (HTTP webhook or MQTT topic) for the + application to send metrics and receive notifications. + operationId: createSession + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + oneOf: + - $ref: "#/components/schemas/HTTPSessionRequest" + - $ref: "#/components/schemas/MQTTSessionRequest" + discriminator: + propertyName: protocol + responses: + "201": + description: Session created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSessionResponse" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "409": + $ref: "#/components/responses/Conflict409" + "422": + $ref: "#/components/responses/Generic422" + + /sessions/{sessionId}: + get: + tags: + - Session Insights + summary: "Get session by sessionId" + description: | + Retrieve the details of a specific session by its operator-assigned + session ID. + operationId: getSession + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Session detail + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Session" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + + delete: + tags: + - Session Insights + summary: Delete session + description: | + Delete a session by its operator-assigned session ID. This will stop + all notifications and metrics streaming for the session. + operationId: deleteSession + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + + /retrieve-sessions: + post: + tags: + - Session Insights + summary: Retrieve Session Insights sessions by device + description: | + Retrieve all Session Insights sessions for a given device. + + **Notes:** + - This operation allows retrieving all active or historical sessions associated with a device. + - It uses POST instead of GET to allow passing sensitive device identifiers in the body, per CAMARA guidelines. + - The request must include a `device` object if using a two-legged token. If using a three-legged token, do not provide a `device` as the device is derived from the token. + + operationId: retrieveSessionsByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to get Session Insights session information by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsInput" + required: true + responses: + "200": + description: An array of sessions matching the specified device. Empty array if none found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsOutput" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}/metrics: + post: + tags: + - Session Insights + summary: Send session metrics + description: | + Stream application-level KPIs (e.g., latency, jitter, throughput, loss) + to the network operator for the specified session. This is used to + evaluate session quality and trigger notifications if thresholds are + breached. + operationId: sendSessionMetrics + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/MetricsPayload" + responses: + "204": + description: Metrics accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + "422": + $ref: "#/components/responses/Generic422" + +components: + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + SessionId: + description: Session ID in UUID format + type: string + format: uuid + + SessionRequest: + description: | + Request body for creating a new session. The session is created under + an existing Application Profile, which defines the expected + performance thresholds and other parameters. + + The operator allocates a sink (HTTP webhook or MQTT topic) for the + application to send metrics and receive notifications. + type: object + properties: + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationSessionId: + type: string + description: | + Optional app-level meeting / match / stream ID used for correlation. + example: "meet-12345" + protocol: + $ref: "#/components/schemas/Protocol" + types: + type: array + items: + $ref: "#/components/schemas/EventType" + required: + - applicationProfileId + - device + - applicationServer + - protocol + - subscribedEventTypes + + SessionBase: + type: object + properties: + id: + type: string + description: Operator-assigned session ID + example: "op-sess-abc123" + applicationSessionId: + type: string + description: Application-provided session reference + example: "meet-12345" + device: + $ref: "#/components/schemas/DeviceResponse" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + description: | + • HTTP → webhook URL (from request) + • MQTT → quality topic (allocated by operator) + subscribedEventTypes: + type: array + items: + $ref: "#/components/schemas/EventType" + startTime: + type: string + format: date-time + expiresAt: + type: string + format: date-time + required: + - id + - device + - applicationServer + - protocol + - sink + - subscribedEventTypes + - startTime + + HTTPSettings: + type: object + description: No additional settings + + MQTTSettings: + type: object + required: [brokerUri, metricsTopic, qualityTopic, qos] + properties: + brokerUri: + type: string + format: uri + metricsTopic: + type: string + description: Topic the **application PUBLISHES** KPI messages to + example: session/op-sess-abc123/appSession/meet-12345/metrics + qualityTopic: + type: string + description: Topic the **application SUBSCRIBES** to for CloudEvents + example: session/op-sess-abc123/appSession/meet-12345/quality + qos: + type: integer + enum: + - 0 + - 1 + retain: + type: boolean + default: false + messageExpiryInterval: + type: integer + + HTTPSessionRequest: + allOf: + - $ref: "#/components/schemas/SessionRequest" + - type: object + properties: + sink: + type: string + description: Webhook URL for event delivery + sinkCredential: + type: string + description: Optional credential for HTTP callbacks + required: + - sink + + MQTTSessionRequest: + allOf: + - $ref: "#/components/schemas/SessionRequest" + - type: object + properties: + sinkCredential: + type: string + description: Credential for MQTT broker access + + HTTPSession: + allOf: + - $ref: "#/components/schemas/SessionBase" + - type: object + properties: + protocol: + type: string + enum: + - "HTTP" + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + MQTTSession: + allOf: + - $ref: "#/components/schemas/SessionBase" + - type: object + properties: + protocol: + type: string + enum: + - "MQTT3" + - "MQTT5" + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + Session: + oneOf: + - $ref: "#/components/schemas/HTTPSession" + - $ref: "#/components/schemas/MQTTSession" + discriminator: + propertyName: protocol + + CreateHTTPSession: + allOf: + - $ref: "#/components/schemas/HTTPSession" + - type: object + properties: + sinkCredential: + type: string + description: Returned only on creation (HTTP) + + CreateMQTTSession: + allOf: + - $ref: "#/components/schemas/MQTTSession" + - type: object + properties: + sinkCredential: + type: string + description: Broker credential (creation only) + + CreateSessionResponse: + oneOf: + - $ref: "#/components/schemas/CreateHTTPSession" + - $ref: "#/components/schemas/CreateMQTTSession" + discriminator: + propertyName: protocol + + Device: + description: | + End-user equipment able to connect to a network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their + request, the API provider must return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do + not match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers with a + given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + optionally prefixed with '+'. + type: string + pattern: '^\+?[0-9]{5,15}$' + example: "123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + ApplicationServer: + type: object + minProperties: 1 + properties: + domainName: + type: string + ipv4Address: + type: string + format: ipv4 + ipv6Address: + type: string + format: ipv6 + port: + type: integer + + Protocol: + type: string + enum: + - HTTP + - MQTT3 + - MQTT5 + + EventType: + type: string + enum: + - org.camaraproject.session-insights.v0.quality-score + - org.camaraproject.session-insights.v0.network-event + - org.camaraproject.session-insights.v0.proposed-resolution + - org.camaraproject.session-insights.v0.subscription-ends + + # ---------- CloudEvents & data payloads ---------- + CloudEvent: + type: object + properties: + specversion: + type: string + enum: + - "1.0" + id: + type: string + source: + type: string + type: + $ref: "#/components/schemas/EventType" + time: + type: string + format: date-time + datacontenttype: + type: string + default: application/json + data: + type: object + required: + - specversion + - id + - source + - type + - time + - data + + SessionQualityData: + type: object + properties: + upstreamRate: + description: | + The upstream bitrate + allOf: + - $ref: "#/components/schemas/Rate" + downstreamRate: + description: | + The downstream bitrate + allOf: + - $ref: "#/components/schemas/Rate" + packetDelay: + description: | + The packet delay one-way latency between the customer's device + and the gateway from the operator's network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, such as voice calls, + video streaming, and data. + The end-to-end or round trip latency will be about two times this value plus the latency not controlled + by the operator + allOf: + - $ref: "#/components/schemas/Duration" + jitter: + description: | + The variation in round-trip + packet delay for the 99th percentile of traffic, following ITU Y.1540 + standards. It considers only acknowledged packets in a session, which are + packets that receive a confirmation of receipt from the recipient (e.g., + using TCP). This requirement helps maintain consistent latency, essential + for real-time applications such as VoIP, video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + packetErrorLossRate: + type: integer + description: | + This field specifies the measured level of data loss during transmission. + The value is an exponent of 10, so a value of 3 means that up to 10⁻³, or 0.1%, of the + data packets may be lost. This setting is part of a broader system that categorizes + different types of network traffic (like phone calls, video streams, or data transfers) + to ensure they perform reliably on the network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + resolution: + type: string + score: + type: integer + required: + - packetDelay + - jitter + - packetErrorLossRate + - downstreamRate + - upstreamRate + - resolution + - score + + ScoreAlertData: + type: object + properties: + score: + type: integer + threshold: + type: integer + severity: + type: string + enum: + - warning + - critical + required: + - score + + ResolutionProposedData: + type: object + properties: + resolutionType: + type: string + enum: + - NETWORK_QOS + - APPLICATION_CONFIG + - OTHER + description: + type: string + required: + - resolutionType + - description + + SubscriptionEndsData: + type: object + properties: + reason: + type: string + + SessionQualityNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.quality-score + data: + $ref: "#/components/schemas/SessionQualityData" + + ScoreAlertNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.network-event + data: + $ref: "#/components/schemas/ScoreAlertData" + + ResolutionProposedNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.proposed-resolution + data: + $ref: "#/components/schemas/ResolutionProposedData" + + SubscriptionEndsNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.subscription-ends + data: + $ref: "#/components/schemas/SubscriptionEndsData" + + NotificationEvent: + oneOf: + - $ref: "#/components/schemas/SessionQualityNotification" + - $ref: "#/components/schemas/ScoreAlertNotification" + - $ref: "#/components/schemas/ResolutionProposedNotification" + - $ref: "#/components/schemas/SubscriptionEndsNotification" + discriminator: + propertyName: type + + MetricsPayload: + type: object + description: KPI message published to `metricsTopic` + properties: + latency: + type: number + format: float + jitter: + type: number + format: float + packetLoss: + type: number + bitrate: + type: number + resolution: + type: string + required: + - latency + - jitter + - packetLoss + - bitrate + - resolution + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + Duration: + description: Specification of duration + type: object + properties: + value: + description: Quantity of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + ErrorInfo: + type: object + properties: + status: + type: integer + code: + type: string + message: + type: string + required: + - status + - code + - message + + RetrieveSessionsInput: + description: Parameters to get QoS session information by device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveSessionsOutput: + description: QoS session information for a given device + type: array + items: + $ref: "#/components/schemas/Session" + minItems: 0 + + + responses: + BadRequest400: + description: Bad request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + Forbidden403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + NotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Conflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS +``` diff --git a/marked/SessionInsights/documentation/API_documentation/SessionInsights_User_Story/raw.md b/marked/SessionInsights/documentation/API_documentation/SessionInsights_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..83c024671f55e31e4755e08467cfd09c12d4a1bb --- /dev/null +++ b/marked/SessionInsights/documentation/API_documentation/SessionInsights_User_Story/raw.md @@ -0,0 +1,15 @@ +# Session Insights (SI) User Story + +| **Item** | **Description** | +| ------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **_Summary_** | As an application developer, I want to be able to stream my application's network KPIs to the network operator. This allows the network operator to monitor in real-time whether it is meeting these dynamic requirements, and if not, proactively suggest or implement corrective measures to maintain optimal performance. | +| **_Roles, Actor(s) and scope_** | **Roles:** API Consumer:Developer

                              **Actors:** Application service providers, hyperscalers, application developers.

                              **Scope:**
                              • Create a Session Insights session
                              • Send Network KPIs
                              • Get Session Insights score
                              • Get root cause and recommended corrective actions
                              • End Session
                              | +| **_Pre-conditions_** | The preconditions are:
                              1. Customer:Developer is eligible to use the Session Insights API, i.e. the Customer has successfully subscribed to the Session Insights API on the platform of an API Provider.
                              2. The customer application has requested and received an access token for the required scopes of the API.
                              3. The application developer has provisioned an application profile that will be used for the Session Insights session.
                              | +| **_Begins when_** | The customer application creates a Session Insights session using an application profile, device identifier or 3-legged token, and callback URI. The CSP provides a session ID in the response. | +| **_Step 1_** | The customer application periodically sends its network KPIs for its session to the CSP either via HTTP post or via MQTT. | +| **_Step 2_** | The CSP calculates a Session Insights score using a combination of the KPIs sent to it from the application along with its own network KPIs and the application profile. The CSP then sends a score back to the customer application via the callback URI provided (could be HTTP webhook, MQTT topic, or other method). | +| **_Step 3_** | The CSP can optionally include additional information along with the score to help diagnose and correct an issue when the score falls below acceptable thresholds (Root Cause). | +| **_Step 4_** | The customer application decides whether to take corrective action. | +| **_Ends when_** | The customer application ends the Session Insights session ends or times out due to inactivity. | +| **_Post-conditions_** | The customer application was able to adjust to network issues in real-time and provide consistent performance to the end user of the application. | +| **_Exceptions_** | Several exceptions might occur during the Session Insights API operations:
                              • Unauthorized: Not valid credentials (i.e. use of an expired access token).
                              • Conflict: Internal configuration policies didn’t allow for operations, i.e. a second Session Insights session for one device.
                              • Not Found: application profile provided for session is not a defined application profile
                              • Bad Request: If KPIs provided are not valid
                              • Session-not-created: Due to other internal errors, Session Insights session resource could not be created. | diff --git a/marked/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist/raw.md b/marked/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ee369a4a83559b66d5942158671aa049de9b5eaf --- /dev/null +++ b/marked/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for api-name api-version in rx.y. + +| Nr | API release assets | alpha | release-candidate | initial
                                public | stable
                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/session-insights.yaml](/code/API_definitions/session-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | Comm. release nr | +| 3 | Guidelines from ICM applied | O | M | M | M | tbd | ICM release nr | +| 4 | API versioning convention applied | M | M | M | M | tbd | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/SessionInsights_User_Story.md](/documentation/API_documentation/SessionInsights_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | N | | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | issue link | +| 10 | API release numbering convention applied | M | M | M | M | tbd | | +| 11 | Change log updated | M | M | M | M | tbd | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | comment | +| 13 | API description (for marketing) | O | O | M | M | Y | [https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/94011619/SessionInsights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/94011619/SessionInsights) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/ShortMessageService/README/raw.md b/marked/ShortMessageService/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8b36ff4146ccef24683a7f021ea43f1c036ac3fb --- /dev/null +++ b/marked/ShortMessageService/README/raw.md @@ -0,0 +1,42 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#285](https://github.com/camaraproject/APIBacklog/issues/285) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase C – Repository With Partial Progress](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# ShortMessageService + +Sandbox API Repository to describe, develop, document, and test the ShortMessageService Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/wSne) + +## Scope +* Service APIs for “Short Message Service” (see APIBacklog.md) +* It provides the customer with the ability to: + * to send SMS to the destination address(es). There are 3 different categories of SMS i.e. Service, Promotional & Transactional. This API is used to send all categories of messages. Pre-requisite for using this API is that SMS Sender application / enterprise (or customer) needs to onboard itself with the access provider before using this API. This API has only single operation i.e. Send SMS - Provides the capability to deliver SMS to the recepient. In order to the receive delivery receipt separate API to be defined which is to be implemented by the API consumer for sending back the delivery receipt to the 'Send SMS' API consumer in a standardized callback API. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Location: virtually + +## Meetings +* Meetings are held virtually +* Schedule: tbd +* Meeting link: tbd + +## Contributorship and mailing list +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/marked/ShortMessageService/code/API_definitions/README/raw.md b/marked/ShortMessageService/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/ShortMessageService/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/ShortMessageService/code/API_definitions/SMS/raw.md b/marked/ShortMessageService/code/API_definitions/SMS/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..237f93a508cbbb4ca62a250d4530b14633dd8e47 --- /dev/null +++ b/marked/ShortMessageService/code/API_definitions/SMS/raw.md @@ -0,0 +1,272 @@ +# SMS + +```yaml +openapi: 3.0.3 +info: + title: SMS API + description: | + The API provides the customer with the ability to send SMS to the recepient address(es). + Customer can use this API to send SMS in following scenarios: + 1. Application server needs to send text message to a recepient number which is being used on a mobile phone device. There are 3 different categories of text SMS i.e. Service, Promotion & Transaction. + 2. Application server needs to send binary message to a recepient number which is being used on (IoT) device. + + Pre-requisite for using this API is that SMS Sender application / enterprise (or customer) needs to onboard themselves with the access provider before using this API. + This API has single operation to send SMS. + + In order to the receive delivery receipt, separate API to be subscribed by the API consumer for receiving the delivery receipt in a standardized callback API. + + # Authorization and authentication + CAMARA guidelines defines a set of authorization flows which can grant API clients access to the API functionality, as outlined in the document [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md). Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + version: 0.1.0-alpha.1 + termsOfService: http://example.com/terms/ + contact: + name: API Support + url: http://www.example.com/support + email: support@example.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ShortMessageService +servers: + - url: '{apiRoot}/{basePath}' + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: sms/v0alpha1 + description: Base path for the Short Message Service +tags: + - name: Short Message Service + description: API operation to send SMS +paths: + /short-message: + post: + security: + - openId: + - send-sms:short-message + tags: + - Send SMS + summary: Send SMS + description: | + The customer application server makes a request to the SMS API to send SMS message to the destination address. + operationId: send-sms + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Submit a request for sending SMS to the destination address + content: + application/json: + schema: + $ref: '#/components/schemas/MessageRequest' + examples: + MessageRequest: + value: + to: ['+910123456789'] + from: '+919876543210' + category: PROMOTION + message: xxxxxxxxxx + required: true + responses: + '200': + $ref: '#/components/responses/Generic200' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + schemas: + MessageRequest: + type: object + required: + - to + - from + - message + properties: + to: + type: array + description: "The recipients MSISDN" + items: + type: string + from: + type: string + description: "The senders MSISDN" + category: + type: string + enum: ["PROMOTION","SERVICE","TRANSACTION"] + message: + type: string + description: "SMS message" + MessageResponse: + type: object + required: + - msgId + - timestamp + properties: + msgId: + type: string + description: "The SMS messages sent to the recipients are identified by smsnumber are identified." + timestamp: + type: string + format: date-time + description: Timestamp when SMS was delivered. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + ErrorInfo: + type: object + required: + - status + - code + - detail + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + detail: + type: string + description: Detailed error description + responses: + Generic200: + description: OK + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/MessageResponse' + example: + msgId: 56647d96-b3e6-48d2-b93f-ab0d56bdd965 + timestamp: "2024-03-19T12:33:27.070Z" + + Generic400: + description: Problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + detail: Client specified an invalid argument, request body or query param + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + detail: Request not authenticated due to missing, invalid, or expired credentials + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + detail: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + detail: Phone number cannot be deducted from access token context + Generic404: + description: Resource Not Found + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + detail: A specified resource is not found + Generic500: + description: Server error + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + detail: Server error + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + detail: Service unavailable +``` diff --git a/marked/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription/raw.md b/marked/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e01800127fa1e7dd085bce71ac93862941c65674 --- /dev/null +++ b/marked/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription/raw.md @@ -0,0 +1,739 @@ +# sms-delivery-notification-subscription + +```yaml +openapi: 3.0.3 +info: + title: SMS Delivery Notification Subscription + description: | + API to create, retrieve and delete event subscriptions related to a sms delivery operation performed on an associated phone number. + + # Introduction + + With this API, customers can create subscriptions for receiving delivery notification on the requests sent. + + The consumer id in the request gives the identity of the consumer for which call back notification subscription to be enabled. + + Upon successfully creating a subscription, the API will provide an Event Subscription ID, and it will indicate the subscription's expiration date. + + After delivering the SMS, the event subscriber will be notified back to the provided Notification-Url given by the subscription-request. + + SMS delivery notification API could be useful in scenarios such as: + + - Reconciliation (by the API consumer) on the number of messages sent vs delivered. + + # Relevant terms and definitions + + # API Functionality + + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.sms.v0.-status`` - Event triggered when the sms delivery task is completed by the server + + Note: Additionally to these list, ``org.camaraproject.sms.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used when: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the API server has to stop sending notification prematurely + + + + The API exposes following capabilities: + * **/subscriptions**: This endpoint has two operations, one that allows to retrieve the list of SMS delivery event subscriptions and another one to create new event subscriptions. + * **/subscriptions/{subscriptionId}**: This endpoint also has two operations, one that allows to retrieve a particular event subscription by id and another one to delete an event subscription also using the id. + + ## SMS delivery notification subscription + + Theses endpoints allow to manage notification subscription on Send SMS delivery event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows Cloudevents specification. + + It is mandatory in the subscription to provide the event `type` subscribed are several are managed in this API. + + Only one event ``type`` is managed for this API: + - ``org.camaraproject.sms.v0.sms-delivery-status`` - Event triggered when a sms delivery event occurs on the any request given by the consumer + + + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as `POST /{$request.body#/webhook/notificationUrl}` + will be posted by the sim swap resource server to the webhook url provided by notification + listener. + + # Authorization and authentication + + CAMARA guidelines defines a set of authorization flows which can grant API clients access to the API functionality, as outlined in the document [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md). Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0-alpha.1 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/sendsms +servers: + - url: '{apiRoot}/sms-delivery-notification-subscriptions/v0alpha1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: SMS delivery notification subscription + description: Operation to manage event subscription on sms delivery event (swapped) + +paths: + /subscriptions: + post: + tags: + - SMS delivery notification subscription + summary: 'Create a sms delivery event subscription for a given consumer' + description: Create a sms delivery event subscription for a given consumer + operationId: createSMSDeliverySubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - sms-delivery:subscriptions:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateSubscription' + required: true + callbacks: + notifications: + "{$request.body#/webhook/notificationUrl}": + post: + tags: + - Session notifications callback + summary: "Session notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The sim swap server will call this endpoint whenever a swapped event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + STATUS: + $ref: '#/components/examples/STATUS' + SUBSCRIPTION_ENDS: + $ref: '#/components/examples/SUBSCRIPTION_ENDS' + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + security: + - { } + - notificationsBearerAuth: [ ] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionInfo' + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionAsync' + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "409": + $ref: '#/components/responses/Generic409' + "500": + $ref: '#/components/responses/Generic500' + "503": + $ref: '#/components/responses/Generic503' + get: + tags: + - SMS Delivery notification subscription + summary: 'Retrieve a list of SMS Delivery event subscription' + description: Retrieve a list of SMS Delivery event subscription(s) + operationId: retrieveSubscriptionList + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - sim-swap:subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/SubscriptionInfo' + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "500": + $ref: '#/components/responses/Generic500' + "503": + $ref: '#/components/responses/Generic503' + /subscriptions/{subscriptionId}: + get: + tags: + - SMS Delivery notification subscription + summary: 'Retrieve a sms delivery event subscription for a phone number' + description: retrieve event subscription information for a given subscription. + operationId: retrieveSubscription + security: + - openId: + - sim-swap:subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionInfo' + "400": + $ref: '#/components/responses/SubscriptionIdRequired' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + delete: + tags: + - SMS Delivery notification subscription + summary: 'Delete a sms delivery event subscription' + operationId: deleteSubscription + description: delete a given event subscription. + security: + - openId: + - sim-swap:subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionAsync' + "400": + $ref: '#/components/responses/SubscriptionIdRequired' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: '#/components/schemas/SubscriptionId' + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + schemas: + SenderId: + type: string + description: "Identifer for the matching criteria basis which call back would be triggered by the server. In this case it would be the message sender id." + example: 'AD-HDFCBK' + + MsgId: + type: string +# pattern: '^\+[1-9][0-9]{4,14}$' + example: '56647d96-b3e6-48d2-b93f-ab0d56bdd965' + description: "Every request from sender application to send SMS to recepient is acknowledged with a MsgId. This MsgId is sent in the call back." + + Status: + type: string + example: 'SUCCESS' + description: "Every request from sender application to send SMS to recepient is acknowledged with a MsgId. This MsgId is sent in the call back." + enum: + - SUCCESS + - FAIL + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + CreateSubscription: + description: The request for creating a sim swap event subscription + type: object + required: + - webhook + - subscriptionDetail + properties: + subscriptionDetail: + $ref: '#/components/schemas/SubscriptionDetail' + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time in date-time format. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) - Once this number is reached, the subscription ends. -1 means there is no limit. + example: -1 + webhook: + $ref: '#/components/schemas/Webhook' + + Webhook: + description: Webhook information for event channel + type: object + required: + - notificationUrl + properties: + notificationUrl: + type: string + example: "https://application-server.com" + description: https callback address where the event notification must be POST-ed + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: | + OAuth2 token to be used by the callback API endpoint. It MUST be indicated within HTTP Authorization header e.g. Authorization: Bearer $notificationAuthToken + + SubscriptionDetail: + type: object + description: The detail of the requested event subscription + required: + - senderId + - type + properties: + senderId: + $ref: '#/components/schemas/SenderId' + type: + $ref: '#/components/schemas/SmsDeliveryNotificationEventType' + +# CreateSubscriptionDetail: +# description: The detail of the requested event subscription +# type: object +# required: +# - type +# properties: +# msgId: +# $ref: '#/components/schemas/MsgId' +# type: +# $ref: '#/components/schemas/SendSMSEventType' + +# SendSMSEventType: +# type: string +# description: | +# sms-delivery-status - Event triggered when a sms-delivery action is complete and delivery status is to be returned back. + +# enum: +# - org.camaraproject.sms.v0.sms-delivery-status + + SmsDeliveryNotificationEventType: + type: string + description: | + sms-delivery - Event triggered after sms-delivery task is complete. This sms-delivery tasks completion may have status/outcome as success or failure which is returned back in callback to the requestor. + + enum: + - org.camaraproject.sms.v0.sms-delivery-status + + SubscriptionInfo: + description: Represents a sim swaps subscription. + required: + - startsAt + - subscriptionId + allOf: + - $ref: '#/components/schemas/CreateSubscription' + - type: object + properties: + subscriptionId: + $ref: '#/components/schemas/SubscriptionId' + subscriptionDetail: + $ref: '#/components/schemas/SubscriptionDetail' + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time in date-time format. + webhook: + $ref: '#/components/schemas/Webhook' + startsAt: + type: string + format: date-time + description: date time when subscription started + expiresAt: + type: string + format: date-time + description: date time when subscription will expire or expired + required: + - eventSubscriptionId + - type + + SubscriptionAsync: + description: Response for a sim swap operation managed asynchronously (Creation or Deletion) + type: object + properties: + subscriptionId: + $ref: '#/components/schemas/SubscriptionId' + + SubscriptionId: + type: string + description: The event subscription identifier. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - data + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: '#/components/schemas/Source' + type: + $ref: '#/components/schemas/SmsDeliveryNotificationEventType' + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + example: 1.0 + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.sms.v0.sms-delivery-status: '#/components/schemas/EventSimSwap' + org.camaraproject.sms.v0.subscription-ends: '#/components/schemas/EventSimSwapSubscriptionEnds' + + Source: + type: string + format: uri-reference + minLength: 1 + description: "Identifies the context in which an event happened in the specific Provider Implementation." + example: + - https://github.com/cloudevents + - mailto:cncf-wg-serverless@lists.cncf.io + - urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - cloudevents/spec/pull/123 + - /sensors/tn-1234567/alerts + - 1-555-123-4567 + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: '2018-04-05T17:31:00Z' + + EventSimSwap: + description: event structure for swapped event + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/DeliveryStatus' + + EventSimSwapSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + required: + - data + properties: + data: + $ref: '#/components/schemas/SubscriptionEnds' + + DeliveryStatus: + description: Event detail structure for SMS Delivery event. + type : object + required: + - msgId + - subscriptionId + properties: + msgId: + $ref: '#/components/schemas/MsgId' + status: + $ref: '#/components/schemas/Status' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnds: + description: Event detail structure for SUBSCRIPTION_ENDS event + type : object + required: + - msgId + - terminationReason + - subscriptionId + properties: + msgId: + $ref: '#/components/schemas/MsgId' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + + + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: "INVALID_ARGUMENT" + message: "Client specified an invalid argument, request body or query param" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: "UNAUTHENTICATED" + message: "Request not authenticated due to missing, invalid, or expired credentials" + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: "PERMISSION_DENIED" + message: "Client does not have sufficient permissions to perform this action" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: "The specified resource is not found" + Generic409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: CONFLICT + message: "The specified resource is in a conflict" + Generic500: + description: Server error + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: "INTERNAL" + message: "Server error" + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: "UNAVAILABLE" + message: "Service unavailable" + SubscriptionIdRequired: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument, request body or query param" + subscriptionIdRequired: + summary: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + examples: + STATUS: + value: + id: 123655 + source: supertelco.notificationSendServer12 + type: org.camaraproject.sms.v0.sms-delivery-status + specversion: "1.0" + datacontenttype: application/json + data: + msgId: 56647d96-b3e6-48d2-b93f-ab0d56bdd965 + subscriptionId: 2ghy-55gg-7iup-yuo9 + time: 2023-01-18T13:18:23.682Z + + SUBSCRIPTION_ENDS: + value: + id: 123658 + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: +123456789 + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: 2ghy-55gg-7iup-yuo9 + terminationDescription: subscription expire time reached + time: 2023-01-19T13:18:23.682Z +``` diff --git a/marked/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story/raw.md b/marked/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9b03ededbd7fb4fae61332069f803e1f9568a58d --- /dev/null +++ b/marked/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story/raw.md @@ -0,0 +1,13 @@ +**User Story: Send Text SMS from channels/applications to the destination address(es) via network operator. ** +
                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to send SMS from channels/applications to the destination address(es) via network operator. There are 3 different categories of SMS i.e. Service, Promotional & Transactional. This API is used to send all categories of messages. | +| ***Roles, Actors and Scope*** | **Roles:** Application Server (of developer)
                                **Actors:** SMS API Consumer (Application Server, Mobile App, Machine), SMS API Provider (Mobile Network Operator or MNO, Hyperscalers), SMS Destination (Machine, Mobile Device)
                                **Scope:** To send text SMS to the destination address(s) | +| ***Pre-conditions*** |Pre-requisite for using this API are:
                                1. SMS Sender application / enterprise (or customer) is onboarded itself with the access provider before using this API
                                2. SMS Sender application / enterprise (or customer) has the API credentials.
                                | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the SMS API to send text SMS to the destination address.
                                **Ends when:** The destination receives the text SMS.
                                | +| ***Post-conditions*** | The SMS is successfully delivered to the destination address.| +| ***Exceptions*** | Several exceptions might occur during the SMS API operations:
                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                • Not Found: The number provided is not managed by the MNO
                                • Invalid input: Not all mandatory input data to invoke operation (e.g. format not as expected).
                                • Conflict: Internal configuration policies didn’t allow for operations.
                                • Not Allowed: Message sending restricted (DND).
                                | + +

                                \ No newline at end of file diff --git a/marked/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story/raw.md b/marked/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d0d305b67c9ccb0006e94c118ee01d7ca63b622d --- /dev/null +++ b/marked/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story/raw.md @@ -0,0 +1,13 @@ +**User Story: Send binary SMS message to communication module** +
                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to remotely control a product equipped with a communication module, so I want to send a binary SMS message of control commands to it. | +| ***Roles, Actors and Scope*** | **Roles:** Application Developer
                                **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                **Scope:** To send binary SMS message to the destination address of the communication module | +| ***Pre-conditions*** |The preconditions are listed below:
                                1. Application developer has onboarded to MNO API
                                2. Application developer has API credentials
                                | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the SMS API to send binary SMS message to the destination address of the communication module.
                                **Ends when:** The communication module receives the binary SMS message.
                                | +| ***Post-conditions*** | The comand in the binay SMS message works on the application of the product equipped with the communication module.| +| ***Exceptions*** | Several exceptions might occur during the SMS API operations:
                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                • Not Found: The number provided is not managed by the MNO
                                • Invalid input: Not all mandatory input data to invoke operation (e.g. format not as expected).
                                • Conflict: Internal configuration policies didn’t allow for operations.
                                | + +

                                diff --git a/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18/raw.md b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..452c6db868e0a251f42904dfb803edf87e9a1cb1 --- /dev/null +++ b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18/raw.md @@ -0,0 +1,30 @@ +# Short Messaging Service meeting + +#### *January 24, 2024* + +
                                + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla, Gaurav Pandey, Rahul Mehta, Hitesh Dalal | +| KDDI | Tetsuya Chiba | +---- + +
                                + +## Agenda + +1. Introductions +2. Defining Ways Of Working + +
                                + +## Points of Discussion +- Define the User Stories for SMS and then move to defining the API specification + +## AoB + +- Next call schedule: January 24, 2024. diff --git a/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24/raw.md b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4d083d91c514a086de0fbd560ded2c5701106a1a --- /dev/null +++ b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24/raw.md @@ -0,0 +1,32 @@ +# Short Messaging Service meeting + +#### *January 24, 2024* + +
                                + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla, Rahul Mehta, Hitesh Dalal | +| KDDI | Tetsuya Chiba | +---- + +
                                + +## Agenda + +1. Introductions +2. Discussion on the API scope + +
                                + +## Points of Discussion +- Discussion on how this API is different from OTP validation API. +- Agreement on using this API for Binary Message +- Defining 2 User Stories for SMS API (Text & Binary SMS) + +## AoB + +- Next call schedule: January 31, 2024. diff --git a/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31/raw.md b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8da82639303494bfead7442d90a495a154c0e819 --- /dev/null +++ b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31/raw.md @@ -0,0 +1,30 @@ +# Short Messaging Service meeting + +#### *January 31, 2024* + +
                                + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla | +| KDDI | Tetsuya Chiba | +---- + +
                                + +## Agenda + +1. Introductions +2. User Story Discussion + +
                                + +## Points of Discussion +- Alignment on the template for documenting User Stories + +## AoB + +- Next call schedule: February 7, 2024. diff --git a/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07/raw.md b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a6a56696da4d7d660cb7190308a6da8d59f63170 --- /dev/null +++ b/marked/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07/raw.md @@ -0,0 +1,29 @@ +# Short Messaging Service meeting + +#### *January 31, 2024* + +
                                + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla | +| KDDI | Tetsuya Chiba | +---- + +
                                + +## Agenda + +- User Story Discussion + +
                                + +## Points of Discussion +- Walkthrough of the Text Message user story + +## AoB + +- Next call schedule: February 7, 2024. diff --git a/marked/ShortMessageService/documentation/MeetingMinutes/README/raw.md b/marked/ShortMessageService/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..49a5f74619942df51a5ba821e16c6c96a1715def --- /dev/null +++ b/marked/ShortMessageService/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,7 @@ +This README.MD can be deleted when the first file is added to this directory. +24-Jan-2024 + +31-Jan-2024 + +7-Feb-2024 + diff --git a/marked/ShortMessageService/documentation/SupportingDocuments/README/raw.md b/marked/ShortMessageService/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/ShortMessageService/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SimSwap/README/raw.md b/marked/SimSwap/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8b289dc2681a2b433c1bde058a437e9255bba051 --- /dev/null +++ b/marked/SimSwap/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# SimSwap + +Incubating API Repository to evolve and maintain the definitions and documentation of SimSwap Service APIs within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/0jXe) + +## Scope + +* Service APIs for “SimSwap” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * obtain information on any recent SIM pairing change related to the User’s mobile account. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.3](https://github.com/camaraproject/SimSwap/releases/tag/r3.3) (Fall25), with the following API versions: + * **sim-swap-subscriptions v0.3.0** + [[YAML]](https://github.com/camaraproject/SimSwap/blob/r3.3/code/API_definitions/sim-swap-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap-subscriptions.yaml) + * **sim-swap v2.1.0** + [[YAML]](https://github.com/camaraproject/SimSwap/blob/r3.3/code/API_definitions/sim-swap.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SimSwap/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SimSwap/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SimSwap/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/hDze) +* Mailing List: + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/SimSwap/code/API_definitions/sim-swap-subscriptions/raw.md b/marked/SimSwap/code/API_definitions/sim-swap-subscriptions/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1f0c6347f77ec6485d14c6c529a3379fa83b7f6c --- /dev/null +++ b/marked/SimSwap/code/API_definitions/sim-swap-subscriptions/raw.md @@ -0,0 +1,1460 @@ +# sim-swap-subscriptions + +```yaml +openapi: 3.0.3 +info: + title: Sim Swap Subscriptions + description: | + This API provides the customer with the ability to subscribe to event related to a sim swap operation performed on an associated phone number. + + # Introduction + + This API empowers service providers and network operators with a seamless mechanism for managing and monitoring SIM card swaps, a process often used in legitimate device upgrades or replacements but also susceptible to abuse in fraudulent activities. + + # Relevant terms and definitions + + * **SIM swap**: + A SIM swap is a process in which a mobile phone user's current SIM card is deactivated or replaced with a new one. This is typically done by contacting the user's mobile service provider and requesting a new SIM card for various reasons, such as a lost or damaged SIM card, upgrading to a new phone, or changing phone numbers while keeping the same device. + + # API Functionality + + The API exposes following capabilities: + * **/subscriptions**: This endpoint has two operations, one that allows to retrieve the list of Sim Swap event subscriptions and another one to create new event subscriptions. + * **/subscriptions/{subscriptionId}**: This endpoint also has two operations, one that allows to retrieve a particular event subscription by id and another one to delete an event subscription also using the id. + + ## Sim Swap notification subscription + + Theses endpoints allow to manage notification subscription on Sim Swap event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows Cloudevents specification. + + It is mandatory in the subscription to provide the event `types` subscribed are several are managed in this API. + + Only one event ``types`` is managed for this API: + - ``org.camaraproject.sim-swap-subscriptions.v0.swapped`` - Event triggered when a sim swap occurs on the associated phoneNumber + + + Note: Additionally to these list, ``org.camaraproject.sim-swap-subscriptions.v0.subscription-ended`` notification `types` is sent when the subscription ends. + This notification does not require dedicated subscription. + It is used when: + - the subscription expiration time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the API server has to stop sending notification prematurely + - the Access Token sinkCredential expiration time (set by the requester) has been reached + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as `POST /{$request.body#/sink}` + will be posted by the sim swap resource server to the webhook url provided by notification + listener. + + ### Data Minimization + + #### phoneNumber presence: + These rules apply for subscription: + + - If 3-legged access token is used, the POST and GET{id} requests & responses must NOT provide the ``phoneNumber``. For GET (list) only subscription(s) for this exactly phone number is/are retrieved (implicit filtering). + - If 2-legged access token is used, for POST and GET{id}, the presence of ``phoneNumber`` in the request & response is mandatory. For GET (list) the device identifier (``phoneNumber``) could be used as filtering criteria. + + #### sinkCredential presence: + + ``sinkCredential`` is only present in POST request and not provided in POST or GET response. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the provider of the application consuming the API and the operator's API exposure platform, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ +servers: + - url: '{apiRoot}/sim-swap-subscriptions/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Sim Swap Subscription + description: Operation to manage event subscription on sim swap event (swapped) + +paths: + /subscriptions: + post: + tags: + - Sim Swap Subscription + summary: 'Create a sim swap event subscription for a phone number' + description: Create a sim swap event subscription for a phone number + operationId: createSimSwapSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - sim-swap-subscriptions:org.camaraproject.sim-swap-subscriptions.v0.swapped:create + + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + SUBSCRIPTION_REQUEST: + $ref: '#/components/examples/SUBSCRIPTION_REQUEST' + SUBSCRIPTION_REQUEST_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_REQUEST_3LEGS' + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The sim swap server will call this endpoint whenever a swapped event occurs. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + SWAPPED: + $ref: '#/components/examples/SWAPPED' + SUBSCRIPTION_ENDS: + $ref: '#/components/examples/SUBSCRIPTION_ENDS' + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + SUBSCRIPTION_RESPONSE: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE' + SUBSCRIPTION_RESPONSE_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE_3LEGS' + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Sim Swap Subscription + summary: 'Retrieve a list of sim swap event subscription' + description: Retrieve a list of sim swap event subscription(s) + operationId: retrieveSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - sim-swap-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + SUBSCRIPTIONS: + $ref: '#/components/examples/SUBSCRIPTIONS' + SUBSCRIPTIONS_3LEGS: + $ref: '#/components/examples/SUBSCRIPTIONS_3LEGS' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Sim Swap Subscription + summary: 'Retrieve a sim swap event subscription for a phone number' + description: retrieve event subscription information for a given subscription. + operationId: retrieveSubscription + security: + - openId: + - sim-swap-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + SUBSCRIPTION: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE' + SUBSCRIPTION_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE_3LEGS' + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Sim Swap Subscription + summary: 'Delete a sim swap event subscription' + operationId: deleteSubscription + description: delete a given event subscription. + security: + - openId: + - sim-swap-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Sim swap notification subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + SubscriptionRequest: + description: The request for creating a sim swap event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible for subscription: + - org.camaraproject.sim-swap-subscriptions.v0.swapped: receive a notification when a sim swap is performed on the line. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + SubscriptionEventType: + type: string + description: | + swapped - Event triggered when a sim swap occurs on the line + enum: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime` or `subscriptionMaxEvents` to limit subscription lifetime. + Event type attributes must be defined in `subscriptionDetail` + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2025-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. With the current API version the type MUST be set to ACCESSTOKEN." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + required: + - phoneNumber + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + + CreateSubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + + SimSwapNotificationEventType: + type: string + description: | + swapped - Event triggered when a sim swap was performed for this phone number + + - subscription-started: Event triggered when the subscription starts + - subscription-updated: Event triggered when the subscription is updated + - subscription-ended: Event triggered when the subscription ends + enum: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + - org.camaraproject.api-name.v0.subscription-started + - org.camaraproject.api-name.v0.subscription-updated + - org.camaraproject.sim-swap-subscriptions.v0.subscription-ended + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible for subscription: + - org.camaraproject.sim-swap-subscriptions.v0.swapped: receive a notification when a sim swap is performed on the line. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: "#/components/schemas/SubscriptionId" + startsAt: + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its metainformation is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/SimSwapNotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.sim-swap-subscriptions.v0.swapped: '#/components/schemas/EventSimSwap' + org.camaraproject.sim-swap-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.sim-swap-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.sim-swap-subscriptions.v0.subscription-ended: '#/components/schemas/EventSubscriptionEnded' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened, as a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventSimSwap: + description: event structure for event sim swapped + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/Swapped" + + EventSubscriptionStarted: + description: event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + Swapped: + description: Event detail structure for ROAMING_ON & ROAMING_OFF event + type: object + required: + - subscriptionId + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + SWAPPED: + value: + id: "123655" + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap-subscriptions.v0.swapped + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: "+123456788" + subscriptionId: 2ghy-55gg-7iup-yuo9 + time: 2023-01-18T13:18:23.682Z + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: 2ghy-55gg-7iup-yuo9 + terminationDescription: subscription expire time reached + time: 2023-01-19T13:18:23.682Z + + SUBSCRIPTION_REQUEST: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionMaxEvents: 10 + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + SUBSCRIPTION_REQUEST_3LEGS: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + SUBSCRIPTION_RESPONSE: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTION_RESPONSE_3LEGS: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTIONS: + value: + - protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTIONS_3LEGS: + value: + - protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED +``` diff --git a/marked/SimSwap/code/API_definitions/sim-swap/raw.md b/marked/SimSwap/code/API_definitions/sim-swap/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d4cd7be53767268b9fdfe4d90ac59c1c96b646c5 --- /dev/null +++ b/marked/SimSwap/code/API_definitions/sim-swap/raw.md @@ -0,0 +1,498 @@ +# sim-swap + +```yaml +openapi: 3.0.3 +info: + title: SIM Swap + description: | + The SIM swap API provides a programmable interface for developers and other users (capabilities consumers) to request the last date of a SIM swap performed on the mobile line, or, to check whether a SIM swap has been performed during a past period. + + # Introduction + + The SIM Swap API performs real-time checks on the last SIM Swap event. + + The SIM Swap API is useful to prevent fraud by reducing the risk of account takeover fraud by strengthening SIM based authentication processes such as SMS One-time passwords. Fraudsters are using SIM swap techniques to intercept SMS messages and reset passwords or receive verification codes that allow them to access protected accounts. + + The SIM Swap API can also be used to protect non-automated actions. For example, when a call center expert contacts a user to clarify or confirm a sensitive operation. + + This API is used by an application to get information about a mobile line latest SIM swap date. It can be easily integrated and used through this secured API and allows SPs (Service Provider) to get this information an easy & secured way. The API provides management of 2 endpoints answering 2 distinct questions: + + * When did the last SIM swap occur? + * Has a SIM swap occurred during last n hours? + + # Relevant terms and definitions + + **SIM swap**: + A SIM swap is a process in which a user's mobile phone number (MSISDN) is associated with a new SIM card (IMSI). This is typically done by contacting the user's mobile service provider and requesting a new SIM card for various reasons, such as a lost or damaged SIM card or upgrading to a new phone. + + SIM swap also happens during other actions like changing user's phone number, changing mobile service provider keeping user's mobile phone number or when activating a new SIM associated to the same phone number, known as multisim service. New subscription is considered as a SIM swap as well, the MSISDN which can be used by another person earlier, is associated with a SIM card it was not associated before. + + # API functionality + + The API provides 2 operations: + + - POST retrieve-date : Provides timestamp of latest SIM swap, if any, for a given phone number. + + - If no swap has been performed and the network operator supports unlimited SimSwap monitoring timeframe, the API will return the SIM activation date (the timestamp of the first time that the SIM connected to the network). + + - If the latest SIM swap date (or the activation date if no SIM swap) cannot be communicated due to local regulations (or MNO internal privacy policies) preventing the safekeeping of the information for longer than the stated period, a `null` value will be returned. Optionally, a `monitoredPeriod` could be provided to indicate monitored time frame (in days) supported by the MNO. In this case the response must be treated as "there were no sim swap events during 'monitoredPeriod'. Either the parameter is optional, it is recommended to support it in SimSwap implementations. + + - POST check: Checks if SIM swap has been performed during a past period (defined in the request with 'maxAge' attribute) for a given phone number. + + - Note: In the specification of the API the 'maxAge' could be between 1 hour to 2400 hours. If this delay is not managed due to the operator's own privacy threshold (which in theory would likely be linked to local regulations in the country) and a request is performed with a value inferior to 2400 but superior to operator policy, then, an error `400 OUT_OF_RANGE `is expected with an explicit message to explain the limitation like `Check monitor period could not exceed local regulations (30 days)`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the provider of the application consuming the API and the operator's API exposure platform, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API. There is 2 ways to retrieve it depending on the authorization flow used: + - When the API is invoked using a two-legged access token, the phone number will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the phone number will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the phoneNumber cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the phoneNumber can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + [GSMA Mobile Connect Account Takeover Protection specification](https://www.gsma.com/identity/wp-content/uploads/2022/12/IDY.24-Mobile-Connect-Account-Takeover-Protection-Definition-and-Technical-Requirements-v2.0.pdf) was used as source of input for this API. For more about Mobile Connect, please see [Mobile Connect website](https://mobileconnect.io/). + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/SimSwap +servers: + - url: "{apiRoot}/sim-swap/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /retrieve-date: + post: + security: + - openId: + - sim-swap:retrieve-date + - openId: + - sim-swap + tags: + - Retrieve SIM swap date + summary: Retrieve SIM swap date + description: Get timestamp of last SIM swap event for a mobile user account provided with phone number. + operationId: retrieveSimSwapDate + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a SIM swap date request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSimSwapDate" + examples: + RETRIEVE_3LEGS: + $ref: "#/components/examples/RETRIEVE_3LEGS" + RETRIEVE_2LEGS: + $ref: "#/components/examples/RETRIEVE_2LEGS" + + required: true + responses: + "200": + description: Contains information about SIM swap change + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SimSwapInfo" + examples: + RETRIEVE_DATE: + $ref: "#/components/examples/RETRIEVE_DATE" + RETRIEVE_MONITORED_PERIOD: + $ref: "#/components/examples/RETRIEVE_MONITORED_PERIOD" + RETRIEVE_MONITORED_NULL: + $ref: "#/components/examples/RETRIEVE_MONITORED_NULL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /check: + post: + security: + - openId: + - sim-swap:check + - openId: + - sim-swap + tags: + - Check SIM swap + summary: Check SIM swap + description: Check if SIM swap has been performed during a past period + operationId: checkSimSwap + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a check SIM swap request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateCheckSimSwap" + examples: + CHECK_3LEGS: + $ref: "#/components/examples/CHECK_3LEGS" + CHECK_2LEGS: + $ref: "#/components/examples/CHECK_2LEGS" + required: true + responses: + "200": + description: Returns whether a SIM swap has been performed during a past period + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckSimSwapInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SimSwapInfo: + type: object + required: + - latestSimChange + properties: + latestSimChange: + type: string + format: date-time + description: Timestamp of latest SIM swap performed. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + monitoredPeriod: + type: integer + description: Timeframe in days for SIM card change supervision for the phone number. It could be valued in the response if the latest SIM swap occurred before this monitored period. + example: 120 + CheckSimSwapInfo: + type: object + required: + - swapped + properties: + swapped: + type: boolean + description: Indicates whether the SIM card has been swapped during the + period within the provided age. + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+346661113334' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + CreateCheckSimSwap: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + maxAge: + type: integer + example: 240 + description: | + Period in hours to be checked for SIM swap. + format: int32 + minimum: 1 + maximum: 2400 + default: 240 + CreateSimSwapDate: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: phone number is not included in the request (in case of 2-legged) or the phone number identification cannot be derived from access token (in 3-legged) + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. + examples: + RETRIEVE_DATE: + summary: Lastest SIM swap date is send back + value: + latestSimChange: 2024-09-18T07:37:53.471829447Z + RETRIEVE_MONITORED_NULL: + summary: Only null value is retrieved + value: + latestSimChange: null + RETRIEVE_MONITORED_PERIOD: + summary: null is send back for the date but a monitoredPeriod is provided + value: + latestSimChange: null + monitoredPeriod: 120 + CHECK_2LEGS: + summary: Check request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + maxAge: 120 + CHECK_3LEGS: + summary: Check request with 3-legged access tokens + value: + maxAge: 120 + RETRIEVE_2LEGS: + summary: Retrieve request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + RETRIEVE_3LEGS: + summary: Retrieve request with 3-legged access tokens + value: + {} +``` diff --git a/marked/SimSwap/documentation/API_documentation/README/raw.md b/marked/SimSwap/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e69de29bb2d1d6434b8b29ae775ad8c2e48c5391 diff --git a/marked/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story/raw.md b/marked/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17dcf08cf4d190f91caeb89150bbdd17aa437db5 --- /dev/null +++ b/marked/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story/raw.md @@ -0,0 +1,11 @@ +# SIM Swap Check API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check if a SIM swap has occurred within a specified period for a user's mobile number so that I can enhance security measures against account takeover fraud. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                **Scope:**
                                - Checks if a SIM swap has occurred within a specified period for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                                1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                2. The ASP:BusinessManager has successfully subscribed to the SIM Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                4. The ASP:User performs an authorization request to CSP
                                5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the SIM Swap API, providing the phone number and the desired period to check for SIM swaps. This request could be done via (or not) the Channel Partner.
                                  **Ends when:** The CSP's SIM Swap server responds indicating whether a SIM Swap has been performed within the specified period. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the SIM based on the SIM Swap information. | +| ***Exceptions*** | Several exceptions might occur during the SIM Swap API operations
                                  - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                  - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| \ No newline at end of file diff --git a/marked/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story/raw.md b/marked/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..6815d94f1d649e80332c54303a0e56a38fe70d82 --- /dev/null +++ b/marked/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story/raw.md @@ -0,0 +1,11 @@ +# SIM Swap Retrieve API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the last SIM swap date for a user's mobile number so that I can enhance security measures against account takeover fraud. | +|***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                  **Scope:**
                                  - Retrieves the timestamp of the last SIM swap event for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                                  1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                  2. The ASP:BusinessManager has successfully subscribed to the SIM Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                  3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                  4. The ASP:User performs an authorization request to CSP
                                  5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                  6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the SIM Swap API, including the phone number provided by the End-User in the ASP:User.
                                    **Ends when:** The CSP's SIM Swap server responds with the timestamp of the last SIM swap event, or the SIM activation date if no swap has occurred. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the SIM based on the SIM Swap information. | +| ***Exceptions*** | Several exceptions might occur during the SIM Swap API operations
                                    - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                    - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).
                                    - Not able to provide: Legal restrictions or data retention policies preventing the retrieval of the requested information.| diff --git a/marked/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist/raw.md b/marked/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3ae826501a4454839ab77ed49fd5157ca6343c77 --- /dev/null +++ b/marked/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist/raw.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for sim-swap 2.1.0 in r3.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                    public | stable
                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](code/API_definitions/sim-swap.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/sim-swap.yaml) | +| 6 | User stories | O | O | O | M | Y | [check](/documentation/API_documentation/SIM-Swap_check_User_Story.md) [retrieve](/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [check](/code/Test_definitions/sim-swap-checkSimSwap.feature) [retrieve](/code/Test_definitions/sim-swap-retrieveSimSwapDate.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [check](/code/Test_definitions/sim-swap-checkSimSwap.feature) [retrieve](/code/Test_definitions/sim-swap-retrieveSimSwapDate.feature) | +| 9 | Test result statement | O | O | O | M | tbd | see [issue #233](https://github.com/camaraproject/SimSwap/issues/233) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | [relative link](https://www.open-gateway.gsma.com/operators-map) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IAPWB) | + +(*) If you encounter issues with the provided test files (.feature), please create an issue in the API Sub-Project to signal these issues so they can be fixed in a patch release. + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist/raw.md b/marked/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..90d9e65b5b4f05e860c30ed80b6978b6cb895258 --- /dev/null +++ b/marked/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for sim-swap-subscriptions 0.3.0 in r3.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                    public | stable
                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](code/API_definitions/sim-swap-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/sim-swap.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/sim-swap-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IAPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..af6513d76499de5c8bfcf60eb7a1e12e47daaba9 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls/raw.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/marked/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1d18cbd060a0403db7ecd0042c2a3a2d2924e1bc --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls/raw.md @@ -0,0 +1,99 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >following items were not presented during meeting, although sharing status and recommendations + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                                    Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                                    + +### NumberVerify + +#### Recommendation: + +**Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design.** +This particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - continue work based on MC Verified MSISDN specification, considering whole service flow. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e8f6f8cccd7405c5255bf635d6a3d64f1e1ded07 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..45341e3ba91317308c5807d9f3a2fe8da281f1da --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cda161c9585539791c3632a5d201527c62ae43e0 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls/raw.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bfd162c5ccdfbca779274c061703d5771d592534 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls/raw.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue #33 - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c5984b1da4f45910db9c99c6b2e6b72851f269ef --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delvered + +### NumberVerify + +- CAMARA & MC APIs yaml files delvered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..22155de9cf8fb5d93e47c0611b518c0b58800fc9 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls/raw.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..313a13075ee7a176dddcaa6188022fad0cdfbe2f --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..63405e4d97b2ee52df13e8d99f7ffdcac17fe96b --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls/raw.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..323c0698a349ea2e2f89c473656b43224bc73938 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls/raw.md @@ -0,0 +1,65 @@ +# Week 38 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1ae1221bfd38f71d6d01facc3fb1d25853123373 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ef2697d8aba24dfdb06e24f959c3107b54eee99e --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls/raw.md @@ -0,0 +1,63 @@ +# Week 44 meeting + +## Participants + +2nd November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Klaus Reifenrath|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toshi Wakayama|KDDI| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. activation date discussion + +> Problem: should it be considered as a sim swap event? + +- makes sense for a multi-sim scenario, when the new sim is activated +- delivering a flag, that informs about using the activation date is an option, although adding new keys in the response body triggers work with Data Privacy, as this would be a new attribute returned in the API response +- this can be country-specific information, therefore might require additional description (inside yaml) +- AP @DT-DawidWroblewski creates a dedicated issue for this problem +2. value on "no event" scenario +- returning "error" should not be considered a good solution, as CSP performs a sim swap check + +> Decision - use "null" value on an event of no sim change, delivered as a value + +2. Notification subscription PR +- work ongoing +- callback URL: should it be a part of developer onboarding? + +### NumberVerification +1. Product naming +2. OpenID Connect vs OAUTH2.0 +- OpenID Connect stays as a Camara preferred security scheme +- it means that */token* response contains tokens: **id_token** & **access_token** +- there is concern about the content of **id token sub value** - requires further discussion +- AP @fernandopradocabrillo - create a PR to fix the description in yaml + + +### OTP Validation + +- no updates + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski create a dedicated issue for a problem: should activation_date be considered as a sim swap event? +2. @fernandopradocabrillo - create a PR to fix description in yaml regarding access_token \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e0da0891dea9b61a037cc429948ba666c8812f95 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls/raw.md @@ -0,0 +1,48 @@ +# Week 46 meeting + +## Participants + +16th November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Klaus Reifenrath|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|ROBERT Ludovic|Orange| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. work towards new release, that is based on v0.5.0 +2. new error message: **403** - PR awaits approval +3. Test cases - make an offline session between TEF & GSMA + +### NumberVerification +1. release version requires fix - accoplish tasks to next version and make a cleanup +2. phone number format discussion - wait for commonalities to provide information what format should be used + +### OTP Validation + + +## AoB + +- discussion about what what API requires to achieve **1.0.0.** + - fixed scopes + - commonalities guidelines + - create release candidate +- discussion about **Camara Winter 2024 release** +- Slack communication channel for informal communication + + +## APs +- @DT-DawidWroblewski review PRs (403 & notification) \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9649060f4797175b13fd85e82675d2dd85862689 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls/raw.md @@ -0,0 +1,60 @@ +# Week 48 meeting + +## Participants + +30th November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Sebastian Köller|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Foo Ming Hui|Singtel| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discusson about sub-project/API name. + + Sugesstion that simSwap might be misleading, as for the audience it is explicit event, when subscriber makes a change of a SIM card. + + In general the scope of API is fine - it delivers a date of a last MSISDN and IMSI pairing, although it would be better to place additional use cases and sim swap scenarios in API description. + +2. X-correlator + + X-correlator header should be a part of all API operators. + +3. Test cases + + waiting for commonalities WG to deliver guidelines about test cases + +### NumberVerification + +1. Discussion about "eligibility check" before triggering Number Verification flow. +2. @DT-DawidWroblewski mentioned about activity in GSMA Authorization Server Authenticator Capabilities (ASAC) group, where community discuss about eligibility check and seamless authenticator capabilities. + +[Link to join](https://myaccess.microsoft.com/%40MemberGateway.onmicrosoft.com#/access-packages/6658a7c4-7b25-4731-a3bc-b9bd7af7d2b1) +[Link to group](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + +### OTP Validation +- no updates + +----- + +## AoB + +- no AoB + +## APs +* AP1 @gregory1g creates a PR to simSwap API that adds new description and use cases for simSwap event +* AP2 @fernandopradocabrillo creates a PR to add x-correlator to simSwap API +* \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..eccf6fad3e79f8aed4645c42d6fbabcf02558de5 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls/raw.md @@ -0,0 +1,60 @@ +# Week 50 meeting + +## Participants + +14 December 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|ROBERT Ludovic|Orange| +|3|Toyeeb Rehman|GSMA| +|4|Gregory Liokumovich|Ericsson| +|5|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about returned objects, while API cannot provide a legitimate response + * if simSwap date is unavailable and service completed runtime, API should return object back to developer stating this fact + * current API design enables followng return options: + - ${date-time} + - null + - empty response + * conclusion is that it is up to business side to decide what should be returned +2. Test cases + * waiting for Commonalities WG guidelines + +### NumberVerification +1. Discussion about phone number format + * phone number pattern revieled in QoD sub-project + * discussion has been taken over to commonalities + * awaiting for commonalities guideline (@bigludo7 shares a link to discussion) + * check with +2. ad + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. Further assessment has to be performed to check if API definition follows commonalities guidelines with regards to status codes & messages + +## AoB + +1. OAS Linting + * check if simSwap, NumberVerification, OTPValidation projects can follow OAS linting + * topic triggered in [NumberVerificatio issue #75](https://github.com/camaraproject/NumberVerification/issues/75) +2. CSP definition + * sub-projects has to follow a common Camara glossary + * currently readers might experience confusion, when checking acronyms used in Camara, e.g. CSP can be defined as Communications Service Provider, but also as Cloud Service Provider +3. Discussion about Camara OIDC Profile, that is planned to be designed in 2024 + * should add more clarity to AuthN/AuthZ concept + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @trehman-gsma - adds a comment about conclusion from meeting inside [#16](https://github.com/camaraproject/SimSwap/issues/16) diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f99cf3cffeb305aa4df198b476dd7a51917332ea --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls/raw.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9d9df6609c0c1b5dcacf2c626ccb3c475a4c8aa9 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls/raw.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..501c50c324316b15642af656e03999e08cca9058 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls/raw.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fc346b5fddbbc2c9802739dffca35566e6b015ba --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls/raw.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b41e7dea57901679e833a8ecbcad79b863f8a25f --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls/raw.md @@ -0,0 +1,42 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB + +* discussion about MWC 2024 +* add commits to sub-projects for next release + +## APs diff --git a/marked/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md b/marked/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..a679824263eaab80ea5f81ba640492098b11118b --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls/raw.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/marked/SimSwap/documentation/MeetingMinutes/README/raw.md b/marked/SimSwap/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ab1b8bf7de4e87d9d9d26c8fd3fd657735333882 --- /dev/null +++ b/marked/SimSwap/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [SIM Swap Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/SIMSwap) diff --git a/marked/SimpleEdgeDiscovery/README/raw.md b/marked/SimpleEdgeDiscovery/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..09a7be5a10d78b00e93e7afbecd87fd86d489068 --- /dev/null +++ b/marked/SimpleEdgeDiscovery/README/raw.md @@ -0,0 +1,51 @@ + + + + + + + + + +# SimpleEdgeDiscovery + +Incubating API Repository to evolve and maintain the definitions and documentation of SimpleEdgeDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/QwCbBQ) + +## Scope +* Service APIs for “SimpleEdgeDiscovery” (see APIBacklog.md) +* It provides the API Consumer with the ability to: + * Discover the closest edge cloud zone to a given device. + * NOTE: The scope of this API should be limited (at least at the first stage) to 4G and 5G. +* Describe, develop, document, and test the APIs +* Started: June 2022 (as part of [EdgeCloud](https://github.com/camaraproject/EdgeCloud/)) + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/SimpleEdgeDiscovery/releases/tag/r2.2) (Fall25), with the following API versions: + * **simple-edge-discovery v2.0.0** + [[YAML]](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/r2.2/code/API_definitions/simple-edge-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimpleEdgeDiscovery/r2.2/code/API_definitions/simple-edge-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimpleEdgeDiscovery/r2.2/code/API_definitions/simple-edge-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SimpleEdgeDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SimpleEdgeDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings (as part of Edge Cloud Sub Project) + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Schedule: Tuesdays 16h-17 CET, every two weeks. + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/EdgeCloud+Meeting+Minutes). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project [https://lists.camaraproject.org/g/sp-edc](https://lists.camaraproject.org/g/sp-edc). + * A message to the community of this Sub Project can be sent using [sp-edc@lists.camaraproject.org](sp-edc@lists.camaraproject.org). diff --git a/marked/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery/raw.md b/marked/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c6ea305942a95de1ac2ffb65daae243afec9d18c --- /dev/null +++ b/marked/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery/raw.md @@ -0,0 +1,712 @@ +# simple-edge-discovery + +```yaml +--- +openapi: 3.0.3 +info: + title: Simple Edge Discovery + version: wip + x-camara-commonalities: 0.6 + description: | + # Find the closest Edge Cloud Zone + --- + # Summary + + The Simple Edge Discovery API returns the name of the closest operator Edge + Cloud Zone to a particular user device. + + # Purpose + Network operators may host multiple Edge Cloud Zones in a + given territory. Connecting your application to a server on the closest + Edge Cloud Zone means packets travel the shortest distance between + endpoints, typically resulting in the lowest round-trip latency. Note, the + physical (GPS) location of a user device is not a reliable way to determine + the closest Edge Cloud Zone, due to the way operator networks are routed - + so the operator will calculate the Edge Cloud Zone with the + _shortest network path_ to the network-attached device identified in the API + request. + + Once you have the name of the closest Edge Cloud Zone to the user device, + you may: + + * connect the application client on the user device to your application + server instance on that Edge Cloud Zone. Note: the IP address of that + application server instance is not part of the API response, so you will need + to map the edge cloud zone name to the server endpoint IP address you received + when you deployed the server via the cloud provider's API. + * or, if you have no instance on that Edge Cloud Zone, you may wish to + deploy one there using the cloud provider's APIs. + + Note: the provider of the Edge Cloud Zone may be an operator, or a cloud + provider working in partnership with the operator. + + # Usage + + The API may be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet), or by a server. + + There is a single API endpoint: `/retrieve-closest-edge-cloud-zone`. + + To call this endpoint, the API consumer must first obtain a valid OAuth2 token + from the token endpoint, and pass it as an `Authorization` header in the API + request. + + # Identifying the device + + The API returns the closest Edge Cloud Zone to a given device, so that + device needs to be identifiable by the network. This can be achieved either + by passing one or more device identifiers in the request, or, from the + three-legged access token where implemented by the operator. + + ## Passing device identifier(s) in the request + At least one of the following device identifiers must be provided, unless + using a 3-legged access token (see next section): + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + + NOTE1: the network operator might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the + same device. + + NOTE2: for this Commonalities release, we are enforcing that the + `networkAccessIdentifier` is only part of the schema for future-proofing, and + CAMARA does not currently allow its use. After the CAMARA meta-release work + is concluded and the relevant issues are resolved, its use will need to be + explicitly documented in the guidelines. + + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will be + identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier + MUST NOT be provided, as the subject will be uniquely identified from the access + token. + + This approach simplifies API usage for API consumers using a three-legged access + token to invoke the API by relying on the information that is associated with the + access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` + object is not included in the request, then the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` + object is also included in the request, then the server will return an error with the + `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device + is identified by these two methods, as the server is unable to make this comparison. + + # Responses + + ## Success + + A JSON object is returned containing an array with a single member object. + This contains identifiers for the closest Edge Cloud Zone. The HTTP status + code will be`200 OK`. An example response: + + ``` + [ + { + "edgeCloudZoneId": "4gt555-6457-7890-d4he-1dc79f44gb66", + "edgeCloudZoneName": "example zone name", + "edgeCloudProvider": "example zone provider" + } + ] + ``` + * `edgeCloudZoneId` is a UUID for the Edge Cloud Zone. + * `edgeCloudZoneName` is the common name of the closest Edge Cloud Zone to + the user device. + * `edgeCloudProvider` is the name of the operator or cloud provider of + the Edge Cloud Zone. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore + the API specification may not document some non-mandatory error statuses as + indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated + to this API version for a complete list of error responses. The applicable + Commonalities Release can be identified in the `API Readiness Checklist` document + associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error + response if it is explicitly documented in the API. + + # Notes for Simple Edge Discovery API publishers + + Should your implementation require the `Port` value to be passed in addition + to the `IP-Address`, please make that explicit in the documentation, and + utilise the `GENERIC_400_MISSING_PORT` error if the `Port` header is omitted. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the provider of the application consuming + the API and the operator's API exposure platform, taking into account the + declared purpose for accessing the API, whilst also being subject to the + prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Further info and support + --- + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/EdgeCloud + +servers: + - url: "{apiRoot}/simple-edge-discovery/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by the service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Discovery + description: | + Find the closest Edge Cloud Zone to the user device. + +paths: + /retrieve-closest-edge-cloud-zone: + post: + security: + - openId: + - simple-edge-discovery:read + operationId: readClosestEdgeCloudZone + parameters: + - in: header + name: x-correlator + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: "#/components/responses/200Success" + "400": + $ref: "#/components/responses/Generic401" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + tags: + - Discovery + summary: | + Returns the name of the Edge Cloud Zone closest to user device + identified in the request. + description: | + On receiving this request, the network will return the name + of the Edge Cloud Zone with the shortest network path to the end user + device identified in the request. + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a combination + of the value of the Edge Resource Name object and the value of the + Provider object (the name of the cloud provider or operator hosting that + edge cloud zone). + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + + + EdgeCloudZoneId: + description: | + Operator-issued UUID for the Edge Cloud Zone. + type: string + format: uuid + additionalProperties: false + + EdgeCloudZoneName: + description: | + Edge Cloud Zone Name - the common name for the Edge Cloud Zone. + type: string + additionalProperties: false + + EdgeCloudProvider: + description: | + The company name of the Edge Cloud Zone provider. + type: string + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represents + + RequestBody: + description: Common request body to allow optional Device object to be passed + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE 1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + NOTE 2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "84.125.93.10", + "publicPort": 59765 + } + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 1024 + maximum: 65535 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + DeviceResponseBody: + description: | + The optional device identifier to include in the response + properties: + device: + description: | + The device identifier that was used to fulfil the request. + If this property is not present then the device + identifier sent in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + + responses: + 200Success: + description: 200 OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + allOf: + - $ref: "#/components/schemas/EdgeCloudZone" + - $ref: "#/components/schemas/DeviceResponseBody" + examples: + Closest Edge Cloud details: + description: The details of the closest Edge Cloud Zone + value: + edgeCloudZoneId: "f81d4fae-7dec-11d0-a765-00a0c91e6bf6" + edgeCloudZoneName: "UK-SOUTH" + edgeCloudProvider: "Example Provider" + Closest Edge Cloud plus device identifier: + description: The details of the closest Edge Cloud Zone + and the device identifier used to fulfill the request + value: + edgeCloudZoneId: "f81d4fae-7dec-11d0-a765-00a0c91e6bf6" + edgeCloudZoneName: "UK-SOUTH" + edgeCloudProvider: "Example Provider" + device: + phoneNumber: "+123456789" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached. + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + {} + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" +``` diff --git a/marked/SimpleEdgeDiscovery/documentation/API_documentation/README/raw.md b/marked/SimpleEdgeDiscovery/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SimpleEdgeDiscovery/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story/raw.md b/marked/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..edddaad50dad1e3ed4ebb089ad2e16f5023319e8 --- /dev/null +++ b/marked/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story/raw.md @@ -0,0 +1,48 @@ +# Simple Edge Discovery API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to discover (using either my application server/backend service, or an HTTPS application client on the end-user device) the closest Edge Cloud Zone to a given end-user's device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                    **Actors:** Application service providers, network operators, application developers. The API allows a check to see if end-user consent is required: if consent is required, the end-user will be an actor in the consent flow.
                                    + **Scope:** | Get the name of the Edge Cloud Zone closest to a given end-user's device | +| ***Pre-conditions*** |The preconditions are listed below:
                                    1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                    2. The Customer:BusinessManager has successfully subscribed to the Simple Edge Discovery product from the product catalog.
                                    3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                    4. | +| ***Activities/Steps*** | **Starts when:** The customer application server/client makes a an HTTPS POST request to the Simple Edge Discovery API to query the closest Edge Cloud Zone to the target device (an end-user device). The target device is either identified in the 3-legged access token where supported, or explicitly identified in the encrypted POST request body.
                                      **Ends when:** The Simple Edge Discovery API retruns the request information, or an error message. | +| ***Post-conditions*** | Optional - the customer may decide to act upon the information by connecting the end-user application client to the application server instance hosted at the closest Edge Cloud Zone, and/or spin up an application server instance at that closest Edge Cloud Zone if not currently hosted there. | +| ***Exceptions*** | Several exceptions might occur after a request to the Simple Edge Discovery API
                                      - Unauthorized: Invalid credentials (e.g. use of already expired access token).
                                      - Invalid Input: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                      - Forbidden: End user has not consented to device identifier information being provided to the Customer:User
                                      - Service not applicable: the device is not currently attached to an Edge-capable network.
                                      - The network cannot resolve the request due to an internal issue.
                                      - a rate limit/request quota has been exceeded. | + +## API Workflows +### Simple Edge Discovery +#### Scenario 1: request from application developer server or application client on device + +Constraints: +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: browser or app calls API over HTTPS +- Northbound Interface only (no 'UNI' client SDK required) + +Note: +- the Edge Cloud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + Note over API Consumer, Operator: PRE device attached
                                      to operator network + Note over API Consumer, Operator: PRE App developer registered,
                                      authenticated and authorised + alt device identified by 3-legged access token + API Consumer->>Operator: POST /retrieve-closest-edge-cloud-zone + Operator->>Operator: calculate closest Edge Cloud Zone for device + Operator->>API Consumer: edgeCloudZoneID, edgeCloudZoneName, edgeCloudZoneProvider + else device identifier(s) passed in request body + API Consumer->>Operator: POST /retrieve-closest-edge-cloud-zone {request body: device} + Operator->>Operator: calculate closest Edge Cloud Zone for device + Operator->>API Consumer: edgeCloudZoneID, edgeCloudZoneName, edgeCloudZoneProvider, device + end + opt Application developer has a local mapping of server endpoints to Edge Cloud Zone names + Application Developer->>Application Developer: lookup app server endpoint (EdgeCloudZone name) + Application Developer->>Application Client: app server endpoint (IP address:port) + Application Client->>Edge Cloud Zone Provider: connect to app server endpoint (IP address:port) + end + opt spin up instance on closest Edge Cloud Zone + Application Developer->>Edge Cloud Zone Provider: create instance(Edge Cloud Zone) + Edge Cloud Zone Provider->>Application Developer: instance endpoint + Application Developer->>Application Client: instance endpoint + end +``` diff --git a/marked/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist/raw.md b/marked/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..424fd3834098dd02d6d412f912e16660e38b0719 --- /dev/null +++ b/marked/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist/raw.md @@ -0,0 +1,21 @@ +# API Readiness Checklist + +Checklist for simple-edge-discovery v2.0.0 + +| Nr | API release assets | alpha | release-candidate | initial
                                      public | stable
                                      public | Status | Comments | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/simple-edge-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see [issue #128](https://github.com/camaraproject/SimpleEdgeDiscovery/issues/128) | +| 10 | API release numbering convention applied | M | M | M | M | Y | Y | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/t4HVB) | + +(1) Certified companies can be found at the [GSMA Open Gateway Portal](https://www.open-gateway.com) diff --git a/marked/SimpleEdgeDiscovery/documentation/SupportingDocuments/README/raw.md b/marked/SimpleEdgeDiscovery/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SimpleEdgeDiscovery/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SiteToCloudVPN/README/raw.md b/marked/SiteToCloudVPN/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c0faff7c4d434fa84569f6dfa4b819d0f5d69684 --- /dev/null +++ b/marked/SiteToCloudVPN/README/raw.md @@ -0,0 +1,42 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#284](https://github.com/camaraproject/APIBacklog/issues/284) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase C – Repository With Partial Progress](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# SiteToCloudVPN + +Sandbox API Repository to describe, develop, document, and test the SiteToCloudVPN Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KC3e) + +## Scope +* Service APIs for “Site To Cloud VPN” (see APIBacklog.md) +* It provides the customer with the ability to: + * Instead of ordering a private or customized network service by phone call, or through customer manager manually, this API allows users to create and configure site to cloud network service according to the user request by one click. With the proposed API, when someone calls the API service with network SLA requirements, telecom operators can create non-public cloud leased network service by orchestrating the IP VPN connections of metropolitan network and/or backbone network. + * S2C VPN API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services. Currently most of the use cases are in the field of industries, finance, education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Location: virtually + +## Meetings +* Meetings are held virtually +* Schedule: Schedule: Biweekly on Friday, 17:50-18:30(GMT+08:00) CST / 11:50-12:30 CET +* Meeting link: https://teams.live.com/meet/9559310154416?p=X9GldgzTnpV6NUdx / Meeting ID: 955 931 015 441 6 & PWD:V2RXNd + +## Contributorship and mailing list +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/marked/SiteToCloudVPN/code/API_definitions/README/raw.md b/marked/SiteToCloudVPN/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..04313f153aeff65f43b757c99d7f1296cfbf3183 --- /dev/null +++ b/marked/SiteToCloudVPN/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/marked/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_/raw.md b/marked/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c4506426fd5d99bdc45f539b41935da6bb1544b8 --- /dev/null +++ b/marked/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_/raw.md @@ -0,0 +1,932 @@ +# S2CVPN3_2_ + +```yaml +openapi: "3.0.3" +info: + title: S2C VPN API + description: | + ##### Before starting to use the API, the developer needs to know about the below specified details : + * S2C VPN service endpoint The URL pointing to the RESTful resource of the S2C VPN API. + * Authentication Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the S2C VPN API. + * Identifier for access point Customer Edge (CE) IPv4 addressand/or IPv6 address of the Customer Edge Router. + * Identifier for the endpoint cloud Provider Edge (PE) IPv4 and/or IPv6 address of the Cloud Provider Edge + * Identifier for the application server(AS)IPv4 and/or IPv6 address of the application server (cloud virtual machine) + * App-Flow (between the application client and application server) The developer wants to have non public network delivery for the precise application data flow for the application users. + * Duration Duration (in hours) for which the S2C VPN session (between CE and cloud PE) should be created. This parameter is optional. When not specified, a default session duration (e.g. 6 months) is applied. The user may request a termination before its expiration. + * Physical Location Physical location of the Customer Edge Router. + + + NOTE- The private physical link between CE and cloud PE is default deployed for one click calling, otherwise it is required to install the physical link, which is out of the scope of this API. + + version: '0.1' +servers: +- url: https://localhost:8080/webapi + description: develop server +paths: + /S2C_VPN_Assessment: + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + isProtected: + type: bool + description: Is S2C VPN protected + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + solution1: + type: array + items: + $ref: '#/components/schemas/S2CVPNAssessment' + example: + - SLA: A + rent: 100 + - SLA: AA + rent: 500 + - SLA: AAA + rent: 800 + solution2: + type: object + properties: + waitdays: + type: integer + description: the waiting-days until the vpn can be offered + minimum: 1 + SLA: + type: string + enum: + - A + - AA + - AAA + rent: + type: integer + description: "VPN monthly rental " + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + /S2C_VPN : + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/S2CVPNOrder' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + resourceGroupId: + type: string + description: resource group Id + cloudGatewayIP: + type: string + description: cloud gateway IPAddress + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + put: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + serviceID: + type: string + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + SLA: + type: string + enum: + - A + - AA + - AAA + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + title: Successful + type: object + properties: + serviceId: + type: string + GuaranteeBandwidth: + type: string + slaLevel: + type: string + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + get: + parameters: + - $ref: '#/components/parameters/X-Correlator' + - $ref: '#/components/parameters/servceId' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + isProtected: + type: bool + description: Is S2C VPN protected + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + purchasedSLA: + type: string + enum: + - A + - AA + - AAA + purchasedGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + purchasedDuration: + type: integer + description: hours + example: 72 + actualSLA: + type: string + enum: + - A + - AA + - AAA + actualGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + actualLatency: + type: integer + description: ms + example: 10 + actualPacketLostRate: + type: number + description: '%' + example: 0.1% + servicedDuration: + type: integer + description: hours + example: 24 + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + delete: + parameters: + - $ref: '#/components/parameters/X-Correlator' + - $ref: '#/components/parameters/servceId' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + isProtected: + type: bool + description: Is S2C VPN protected + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + actualSLA: + type: string + enum: + - A + - AA + - AAA + actualGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + actualLatency: + type: integer + description: ms + example: 10 + actualPacketLostRate: + type: number + description: '%' + example: 0.1% + servicedDuration: + type: integer + description: hours + example: 24 + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' +components: + parameters: + X-Correlator: + name: X-Correlator + required: true + in: header + description: "Service correlator to make E2E observability,Recommendation is to use UUID for values,for example:b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schema: + type: string + servceId: + name: servceId + required: true + in: query + description: "service session ID" + schema: + type: string + servceName: + name: servceName + required: true + in: query + description: "servce name" + schema: + type: string + isProtected: + name: isProtected + required: true + in: query + description: Is S2C VPN protected + schema: + type: bool + CEType: + name: CEType + required: true + in: query + description: S2C VPN access point type + schema: + type: string + enum: + - site + - cloud + primaryCEIP: + name: primaryCEIP + required: true + in: query + description: primary Access point CE address + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + secondaryCEIP: + name: secondaryCEIP + required: false + in: query + description: secondary Access point CE address. When isProtected is true, secondaryCEIP is required + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + PEType: + name: PEType + required: true + in: query + description: S2C VPN endpoint type ( Cloud PE/gateway type) + schema: + type: string + enum: + - site + - cloud + primaryPEIP: + name: primaryPEIP + required: true + in: query + description: primary Endpoint Cloud PE address + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + secondaryPEIP: + name: secondaryPEIP + required: false + in: query + description: secondary Endpoint Cloud PE address. When isProtected is true, secondaryPEIP is required + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + sla: + name: slaLevel + required: true + in: query + description: "available SLA (Service-Level Agreement)" + schema: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + name: GuaranteeBandwidth + required: true + in: query + description: Guarantee Bandwidth (Mps) + schema: + type: integer + minimum: 1 + duration: + name: duration + required: true + in: query + description: "Guarantee duration, unit:Hour" + schema: + type: integer + CELocation: + name: CELocation + required: true + in: query + description: Access point CE physical location + schema: + type: string + routeProtocal: + name: routeProtocal + required: true + in: query + description: routeProtocal + schema: + type: string + enum: + - static + - BGP + + schemas: + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. + required: + - startDate + ErrorInfo: + type: object + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + required: + - message + - status + - code + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + S2CVPNAssessment: + type: object + properties: + SLA: + type: string + enum: + - A + - AA + - AAA + rent: + type: integer + description: "VPN monthly rental " + S2CVPNOrder: + type: object + properties: + servceName: + type: string + description: "servce name" + isProtected: + type: bool + description: Is S2C VPN protected + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + SLA: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + routeProtocal: + type: string + enum: + - static + - BGP + + responses: + InvalidArgument: + description: Invalid Argument + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_INPUT + message: | + - Expected property is missing: Site or cloud 's ipv4addr/ipv6addr + Conflict: + description: conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: CONFLICT + message: Schema validation failed at ... + AuthenticationRequired: + description: Authentication Required + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required + PermissionDenied: + description: Permission denied + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + NotFound: + description: Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + MethodNotAllowed: + description: Method not allowed + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target + NotAcceptable: + description: Not Acceptable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 406 + code: NOT_ACCEPTABLE + message: The server can't produce a response matching the content requested by the client through Accept-* headers + UnsupportedMediaType: + description: Unsupported Media Type + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Internal: + description: Internal Error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: Unknown server error.Typically a server bug. + BadGateway: + description: Bad Gateway + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 502 + code: BAD_GATEWAY + message: Couldn't reach an upstream internal service. + Unavailable: + description: Service Unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: UNAVAILABLE + message: Service unavailable + Timeout: + description: Timeout + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: Request timeout exceeded +``` diff --git a/marked/SiteToCloudVPN/documentation/API_documentation/README/raw.md b/marked/SiteToCloudVPN/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story/raw.md b/marked/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f29f6abbbdb045a558e8bf99182d42c4b35a0c5b --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story/raw.md @@ -0,0 +1,10 @@ +# SiteToCloud(S2C) VPN API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer or industry customer, I want to request (using my application server/backend service)cloud leased network connection service between siteA/cloudA and siteB/cloudB from a Communication Service Provider (CSP), so that I can ensure better and more reliable quality for our end users at any required time with proper cost. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                      **Actors:** Application service providers, industry customer, application developers.
                                      **Scope:** Site to Cloud VPN Service Booking(check network availability level, resource availability and corresponding fees ) \- Create/Remove/Modify/Query service instance (S2C VPN session resource) | +| ***Pre-conditions*** |The preconditions are listed below:
                                      1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                      2. The Customer:Administrator has onboarded the Customer:User to the platform.
                                      3. The Customer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                                      4. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The customer application server makes a POST request (including required service area(access node and end node ), bandwidth requirements,etc) to the S2C VPN service provision creation API to create a new S2C VPN session resource.
                                        **Ends when:**  The customer application server makes a DELETE request to the S2C VPN service deletion API , or the S2C VPN service deletion session resource deletion was triggered automatically either because the customer specified duration has expired or the default expiration limit set by the S2C VPN service provider has reached. | +| ***Post-conditions*** | The specified App-Flow was provided stable and private network( required bandwidth and latency) connection to computing/storage services on the cloud and if callback URL was specified, a S2C VPN session resource termination notification was received at the end. | +| ***Exceptions*** | Several exceptions might occur during the S2C VPN API operations
                                        - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                        - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                                        - Session-not-created: Due to other internal errors or insufficient resources , S2C VPN session resource could not be created | diff --git a/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12/raw.md b/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..62b4b877bd2a16bd23f072e71b3aca4c719e1864 --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12/raw.md @@ -0,0 +1,29 @@ +# Site To Cloud VPN Meeting - MOM-2024-04-12 + +*Friday, April 12th, 2024* + +## Attendees (probably incomplete) + +* Dan Xu (China Telecom) +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* ... + +## Agenda +* Review API documentation of S2C VPN API pr#11, issues [#8](https://github.com/camaraproject/SiteToCloudVPN/issues/8) +* Review initial Yaml of Site to Cloud VPN API #10, issues [#9](https://github.com/camaraproject/SiteToCloudVPN/issues/9) +* AOB + + + +## Discussion + +1. The scope of the Site To Cloud VPN, for example, for API creation, should the endpoint of Site To Cloud VPN be the cloud provider edge(PE) or the cloud virtual machine? + + Huawei experts pointed that cloud PE is in the management scope of network controllers, while cloud virtual machine is the management scope of cloud management system, so cloud PE as the endpoint will be a easier way to complete the API. + +## AOB +1. The next call will be on Friday, April 26th, 15:30-16:30(GMT+08:00) CST / 9:30-10:30 CET + + \ No newline at end of file diff --git a/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524/raw.md b/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..216ed88a85e8e8acd0133eed5d89b12434df8903 --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524/raw.md @@ -0,0 +1,80 @@ +# Site To Cloud VPN Meeting - MOM-2024-04-12 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) + +* Dan Xu (China Telecom) + +* Shuting Qing (Huawei) + +* Jin Xu (Huawei) + + + +## Agenda +* Discuss the input and output parameters pr#13 +* Dissuss issues [#17](https://github.com/camaraproject/SiteToCloudVPN/issues/17) +* AOB + + + +## Discussion + +* Regarding the description and definition of S2C VPN access point and S2C VPN endpoint, both of them can be site or cloud, therefore, this API natively support the cloud to cloud connection scenarios. + +* Need to further consider whether more input parameters are needed + +​ + +## Appendix + +Request Body of S2C_VPN_Assessment + +- url: https://localhost:8080/webapi + description: develop server + paths: + /S2C_VPN_Assessment: + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + CEIP: + description: Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + PEIP:: + description: Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + + + diff --git a/marked/SiteToCloudVPN/documentation/MeetingMinutes/README/raw.md b/marked/SiteToCloudVPN/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN/raw.md b/marked/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3ddeb9993aabbfd1c77a10d16edf8c7002d00df4 --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN/raw.md @@ -0,0 +1,11 @@ +| **Field** | Description | +| :---------------------------------------- | ------------------------------------------------------------ | +| API family name | Site to cloud (S2C) VPN | +| API family owner | China Telecom, Huawei | +| API family summary | **High level description**
                                        Instead of ordering a private or customized network service by phone call, or through customer manager manually, this API allows users to create and configure site to cloud network service according to the user request by one click. With the proposed API, when someone calls the API service with network SLA requirements, telecom operators can create non-public cloud leased network service by orchestrating the IP VPN connections of metropolitan network and/or backbone network.
                                        S2C VPN API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services. Currently most of the use cases are in the field of industries, finance, education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc.

                                        **Input params**
                                        service name, access node type, access node ip address, end node type, end node ip address, network availability level, bandwidth, duration, routing protocol, access node GIS address/ID.

                                        **Output params**
                                        API call success or failure response, service Id, resource Id

                                        | +| Technical viability | This API uses existing IP VPN connection creation capabilities of MAN(Metropolitan Area Network) and backbone network in operators. | +| Commercial viability | This API is suitable to multi-sites, industries and applications which require private network service ( large bandwidth, low latency, high guarantee and security), fast and flexible on-demand service provisioning. The original customers can choose traditional product delivery mode or Service on Demand API mode. The new customers will use Service on Demand API mode which is easy to use. | +| YAML code available? | TBD | +| Validated in lab/productive environments? | YES, validated in lab environment | +| Validated with real customers? | No | +| Validated with operators? | No with other operators. | \ No newline at end of file diff --git a/marked/SiteToCloudVPN/documentation/SupportingDocuments/README/raw.md b/marked/SiteToCloudVPN/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements/raw.md b/marked/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..23ad76ec20e9bc00f1d7019e3f45b7c567866846 --- /dev/null +++ b/marked/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements/raw.md @@ -0,0 +1,18 @@ +# Site To Cloud (S2C) VPN + +This API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services for industries and applications such as education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc. + +## Use cases and requirements + +#### Data storage scenarios + +- Overview + + There are two typical application scenarios: + + 1. For backup and storage scenarios of cold data that has not been used for a long time, the data needs to be backed up and stored on a cloud with reliable network connectivity. + 1. When the distributed cloud resources usage rate is unbalanced, local video streams are scheduled to cloud nodes with sufficient resources for storage + +- Requirements: + + - For data storage applications(such as video, voice, and images storage), it is needed to create the stable data transmission network to access cloud resources that meet the storage and network requirements of the application/capability invokers by S2C VPN API. For example, for cloud court application that demands to deliver trial video materials to the central cloud, the network delay is required to lower than 50ms and bandwidth is higher than 20Mbps , so cloud court application is suitable to call S2C VPN API to achieve elastic, private and secure data delivery and storage. \ No newline at end of file diff --git a/marked/SponsoredData/README/raw.md b/marked/SponsoredData/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..aaa7f5d950b985397614a87ebc41e5207b1de9db --- /dev/null +++ b/marked/SponsoredData/README/raw.md @@ -0,0 +1,62 @@ + + + + + + + + + +# SponsoredData + +Sandbox API Repository to describe, develop, document, and test the **Sponsored Data Service API(s)**. This repository currently belongs to the *Sandbox* stage and is under active development within the CAMARA framework. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/f4CVDg) + +## Scope + +The **Sponsored Data** API enables a sponsoring company to cover the data usage of end users for a defined period and/or data volume, thereby strengthening its brand presence and enhancing the user experience. + +The API is organized into three hierarchical levels: + +- **Sponsor:** The company that finances the sponsored data usage. +- **Campaigns:** Sets of sponsorship actions contracted by sponsors for various commercial or marketing purposes. +- **Sponsored Subscribers:** Individual users participating in a campaign, who opt in to receive sponsored data for a defined volume and duration. The sponsorship is always activated upon the user’s explicit choice or consent. + +Campaigns can follow one of two commercial models: + +Campaigns can be organized under different commercial models, depending on the sponsorship agreement between the Sponsor and the Operator: + +- **Prepaid** — The Sponsor pre-purchases a total data volume, from which units are deducted as sponsored sessions are started and consumed. +- **Postpaid** — The Sponsor is billed at the end of the campaign cycle based on the actual sponsored data consumption. + +The API supports the following operations: + +- `/start-sponsorship` +- `/session-status` +- `/revoke-sponsorship` +- `/campaign-status` +- `/active-sponsorships` +- `/configure-alerts` +- `/campaign-management` + +Identifiers such as **Sponsor_Id**, **Campaign_ID** and **Session_ID** are generated and managed by the Operator Platform (MNO). + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-Weekly on Fridays at 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://github.com/camaraproject/SponsoredData/tree/main/documentation/MeetingMinutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/SponsoredData/code/API_definitions/README/raw.md b/marked/SponsoredData/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/SponsoredData/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/SponsoredData/code/API_definitions/sponsored_data/raw.md b/marked/SponsoredData/code/API_definitions/sponsored_data/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ded1a83ae9acf3fbb84b0318b907a51a001a1f3e --- /dev/null +++ b/marked/SponsoredData/code/API_definitions/sponsored_data/raw.md @@ -0,0 +1,1342 @@ +# sponsored_data + +```yaml +openapi: 3.0.3 +info: + title: Sponsored Data API + version: wip + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + description: | + + Sponsored Data API for OpenGateway/CAMARA Project + + The Sponsored Data API allows sponsoring companies (EPs) to cover the cost of mobile data access for end-users on 4G and 5G networks. This API is part of the Open Gateway/CAMARA initiative and provides a set of operations for the dynamic management of mobile data sponsorship. Sponsoring companies can start or revoke sponsorships for users, as well as query the status of both sponsorship sessions and their campaigns. + + The API also allows for the verification of user eligibility for sponsorship and the ability to pause and resume active campaigns. With this API, mobile operators can offer differentiated services that enable innovative business models, providing connectivity at no direct cost to the end-user, with funding provided by a sponsoring entity. + + This service is ideal for advertising campaigns, product promotions, or services. + + Objective of This Initial Version + In this initial version of the API, the sponsorship is proposed for all data traffic (ANY) carried by the user's default bearer, for a specified volume and time, without focusing on a specific destination. + + * Onboarding * + Onboarding is the process by which a Sponsoring Company (EP) contracts a Sponsorship Campaign with the API Gateway Platform (OpenGateway) and the specific Mobile Network Operator (MNO). Initially, this event is supported by the signing of an agreement or documentation outlining the general objectives of the campaign and default sponsorship conditions. For example: + + Type of Campaign: Prepaid or postpaid + Total data volume contracted for prepaid campaigns, e.g., 2000 MB + Campaign validity, e.g., (from/to) or (336 total hours consumed since activation) + Default sponsored data volume for users, e.g., 50 MB + Default sponsorship validity per user, e.g., 10 minutes + Additionally, during this onboarding process, the EP is provided with the "sponsorId" and the specific "campaign_Id". + + * campaignId * + Campaign_ID is a unique identifier assigned to each sponsorship campaign contracted by a Sponsoring Company and assigned during the onboarding process. + + * Traceability - sessionId * + All operations associated with a user (UE) sponsorship are grouped under a session identified by a sessionId. This identifier allows tracking and correlating all interactions within the same sponsorship session. + + * Assignment of Identifiers * + Both, campaign_Id and sessionId, are assigned and managed exclusively by the API Gateway Platforms (OpenGateway) and communicated to both the Sponsoring Companies and the MNOs. CampaignId during the onboarding document signing proccess. And sessionId on real time during each sponsorship operation request. + + * Authorization and Authentication * + The "Camara Security and Interoperability Profile" provides details on how a client requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the Profile. + + The specific authorization flows to be used will be determined during the onboarding process, occurring between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, and subject to the prevailing legal framework dictated by local legislation. + + It is important to note that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + * Authorization and Consent Approach * + The Sponsored Data API facilitates user-initiated sponsorship of data services, requiring active user engagement at specific moments via the sponsor’s application. Given the nature of this service, where users must explicitly request sponsorship, the "Authorization Code Flow - Frontend Flow" has been chosen as the authorization and consent method. This flow aligns with the need for secure, direct interaction between the user and the service, ensuring that consent is explicitly provided in a manner that complies with data protection regulations such as GDPR. + + * API Functionality * + This API exposes the following endpoints: NOTE: All of these are REQUIRED for minimal and correct operation unless explicitly indicated otherwise [OPTIONAL OPERATION] + + /sponsorship: Initiates sponsorship and includes a webhook for session-related notifications. With HTTP 201, the Gateway Platform returns the sessionId. + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/session-status: Queries the status of a particular session. Returns session-related data. + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/revoke: Revokes an active sponsorship session. If active, it must be terminated. + /campaign/{sponsorId}/{campaignId}/status: Queries the status of the campaign, returning whether it is active, paused, or completed. Includes data such as campaign start and end time, consumed data volume, and additional information. The contracted data volume and remaining data volume are included only for prepaid campaigns. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/active-sponsorship-list: Queries the list of users currently sponsored by the campaign. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/alert-subscription: Requests subscription to events associated with the campaign. Includes a webhook for notifications. In this version of the API, only consumption thresholds and expiration events are available. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/manage: Allows pausing and reactivating a campaign. During onboarding, it should be defined whether paused periods consume campaign validity time. [OPTIONAL OPERATION] + + * Date and Time Formats * + All date and time values in this API are represented using the ISO 8601 format. For example, '2023-11-22T13:37:00Z' represents November 22, 2023 at 1:37 PM UTC. + + * Roles * + Mobile Network Operators (MNOs): Providers of mobile services that manage network infrastructure and data provisioning. + Sponsoring Companies (SCs): Companies that fund the use of mobile data for their clients or specific users, aiming to offer a no-cost data experience. + API Gateway Operator Platform (OpenGateway level): A gateway with various functions based on best business practices established by OpenGateway. In addition to translation functions, it must track and manage campaigns and sessions established during operation. + Sponsored Users (SU): Mobile network users whose mobile data usage is sponsored by the EPs. + +servers: + - url: "{apiRoot}/sponsored-data/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Sponsorship Management + description: Operations related to starting, revoking, and monitoring sponsorship sessions. + - name: Campaign Management + description: Operations for managing sponsorship campaigns and alerts. + - name: Reporting + description: Operations for querying balances, usage, and active sessions. + +paths: + + /sponsorship: + post: + tags: + - Sponsorship Management + summary: Start Sponsorship Session Request + description: This operation requests the sponsorship for a subscriber in a specific campaign, allowing them to use sponsored data within the limits set by this request or those defined in the campaign onboarding declaration by default. + operationId: startSponsorship + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + requestBody: + description: Parameters for creating the new sponsorship session + required: true + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + dataVolume: + description: Data volume (in MegaBytes) to be sponsored by the sponsor for the mobile user. If not specified, the default data volume defined in the onboarding rules will apply. + type: integer + minimum: 1 + maximum: 1000 + duration: + description: Duration (in minutes) of the requested sponsorship. If not specified, the duration defined in the onboarding rules will apply. + type: integer + minimum: 1 + maximum: 1440 + webhookUrl: + $ref: '#/components/schemas/WebhookUrl' + callbackToken: + description: Security token for authenticating notifications sent to the webhook. + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" # UUID versión 4 regular expression + required: + - sponsorId + - campaignId + - phoneNumber + - webhookUrl + - callbackToken + callbacks: + notifications: + "{$request.body#/webhookUrl}": + post: + tags: + - Sponsorship notifications callback + summary: "Sponsorship notifications callback" + description: | + This endpoint must be implemented by the API consumer. The sponsorship server will send notifications to this URI when a sponsorship ends, providing the reason for termination and session details + operationId: notifySponsorshipEnd + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/x-callbackToken" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SponsorshipEndNotification" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + responses: + '201': + description: Successful operation. New sponsorship session created. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + + sponsoredDataVolume: + description: The assigned data volume for the user. This value is derived from either the sponsorship request or, if not specified in the request, from the default value defined in the campaign profile during onboarding. + type: integer + minimum: 1 + maximum: 1000 + required: + - sponsorId + - campaignId + - sessionId + - startTime + - endTime + - sponsoredDataVolume + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/session-status: + get: + tags: + - Reporting + summary: Sponsorship Session Status Inquiry + description: | + Queries detailed information about a sponsorship session for a specific campaign and sponsor. + NOTES: + The access token for this query must be a 2-legged token, and the sponsor must have been previously authorized with a 3-legged token at the time of session initiation. + The session must have been created by the same API client indicated in the access token. + operationId: getSessionStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + - name: sessionId + description: Unique identifier of the sponsorship session. + in: path + required: true + schema: + $ref: '#/components/schemas/SessionId' + responses: + "200": + description: Contains information about the sponsorship session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + sessionStatus: + description: Indicates whether the session is active or inactive. + enum: + - active + - inactive + dataVolumeConsumed: + description: Volume of data consumed in the session. (MBytes) + type: integer + dataVolumeAvailable: + description: Volume of remaining available data in the session. (MBytes) + type: integer + endReason: + description: Reason for session termination, if it is no longer active. + enum: + - validity_expired + - data_exhausted + - session_revoked + - not_available + required: + - phoneNumber + - startTime + - endTime + - sessionStatus + - dataVolumeConsumed + - dataVolumeAvailable + examples: + session_active: + description: Session still active + value: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541149924576" + startTime: "2024-09-01T12:00:00Z" + endTime: "2024-09-01T14:00:00Z" + sessionStatus: "active" + dataVolumeConsumed: 60 + dataVolumeAvailable: 40 + endReason: not_available + session_inactive: + description: Session still active + value: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541149924576" + startTime: "2024-09-01T12:00:00Z" + endTime: "2024-09-01T13:03:00Z" + sessionStatus: "inactive" + dataVolumeConsumed: 100 + dataVolumeAvailable: 0 + endReason: data_exhausted + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/revoke: + delete: + tags: + - Sponsorship Management + summary: Revocation of Sponsorship + description: This operation revokes an active sponsorship, preventing further use of sponsored data for the subscriber. + operationId: revokeSponsorship + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + - name: sessionId + description: Unique identifier of the sponsorship session. + in: path + required: true + schema: + $ref: '#/components/schemas/SessionId' + responses: + '200': + description: Session revoked successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + + requestResult: + type: string + enum: + - successful_revocation + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/campaign-status: + get: + tags: + - Reporting + summary: Campaign Status Inquiry [active, paused, concluded], data volume balance. + description: > + Retrieves the current status of a specific sponsorship campaign for a given sponsor. + Provides information such as whether the campaign is active, paused, or completed, along with key metadata like start and end dates, data volume limits, and any configured alerts. This endpoint allows sponsoring companies to monitor the progress and operational state of their campaigns. + operationId: getCampaignStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + responses: + '200': + description: Returns the status of the campaign + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + status: + type: string + description: Current status of the campaign (e.g., "active", "paused", "completed"). + enum: + - active # The campaign is currently ongoing. + - paused # The campaign is temporarily halted. Active sponsorships continue until completion, and the campaign's duration does not extend due to this pause. + - completed # The campaign has finished successfully, either because all contracted data has been consumed or the time limit has been reached. This status could be sufficient to indicate that the campaign has ended. + - not_available + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + campaignType: + description: Indicates whether the campaign is prepaid or postpaid + type: string + enum: + - prepaid + - postpaid + contractedDataVolume: + type: integer + description: Total data volume contracted for the campaign in MegaBytes. This field is REQUIRED only for prepaid campaigns. + usedDataVolume: + type: integer + description: Total data volume consumed in the campaign, in megabytes (MB), as allocated for sponsorships. + remainingDataVolume: + type: integer + description: Remaining data volume available for the campaign in MegaBytes. This field is REQUIRED only for prepaid campaigns. + completionReason: + type: string + description: Reason for completion (e.g., "time expired", "data exhausted"). + enum: + - time_expired + - data_exhausted + - not_available # if the campaign is still active or paused + required: + - sponsorId + - campaignId + - status + - startTime + - endTime + - usedDataVolume + - completionReason + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/active-sponsorships: + get: + tags: + - Reporting + summary: Query of Active Sponsorships + description: > + Returns the list of users currently benefiting from sponsored data under a specific campaign. Each entry includes identifiers and session information to track which end users are actively consuming sponsored data. Useful for reporting and campaign analytics. + operationId: getActiveSponsorships + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + responses: + '200': + description: List of users currently sponsored by the campaign. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + activeSponsorships: + type: array + items: + type: object + properties: + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + totalCount: + description: Total number of sponsored subscribers currently. + type: integer + example: 5000 + example: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + activeSponsorships: + - sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541100000001" + - sessionId: "123e4567-e89b-12d3-a456-426614174003" + phoneNumber: "+541100000002" + - sessionId: "123e4567-e89b-12d3-a456-426614174008" + phoneNumber: "+541100000003" + totalCount: 3 + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/alert-subscription: + post: + tags: + - Campaign Management + summary: Campaigns - Subscription to Alert y Notifications + description: | + This operation enables Sponsors (EPs) to subscribe to receive notifications related to campaigns. With the subscription, the EP provides a webhook URL and a token, which will be used by the API Gateway to send notifications related to the campaign. + In this API version, only two types of alerts are provided: + - Notification for consuming more than 80% of the contracted data volume. + - Notification for campaign validity expiration. + - Notification for campaign data volume exhausted. + - Alerts for network failures will be addressed in future versions. + operationId: configureAlerts + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + webhookUrl: + $ref: '#/components/schemas/WebhookUrl' + callbackToken: + type: string + description: Security token to authenticate notifications sent to the webhook. + alertDataVolumeThresholds: + type: boolean + description: Indicates whether a notification should be sent when data consumption exceeds 80% of the contracted amount (applicable for prepaid campaigns).. + example: true + campaignExpiryNotification: + type: boolean + description: Indicates whether a notification should be sent when the campaign expires. + example: true + dataVolumeExhausted: + type: boolean + description: Indicates whether a notification should be sent when the campaign data volume is exhausted. + example: true + callbacks: + notifications: + "{$request.body#/webhookUrl}": + post: + tags: + - Campaign notifications callback + summary: "Callback definition for campaign notifications (webhookUrl)" + description: > + This endpoint must be implemented by the API consumer. The server will send notifications to this URL with the token provided in the subscription to authenticate the request. + operationId: notifyCampaignEvent + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-callbackToken' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/CampaignNotification" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + notifications: + enum: + - alertDataVolumeThresholds + - campaignExpiryNotification + - dataVolumeExhausted + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + responses: + '200': + description: Campaign notifications subscription - SUCCESS + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + requestResult: + type: string + example: "Campaign notifications subscription - SUCCESS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/management: + post: + tags: + - Campaign Management + summary: Campaign Management + description: > + This operation allows pausing or resuming a campaign based on the action parameter provided in the request body. The possible values for action are: + - PAUSE to temporarily halt new sponsorships (ongoing sponsorships will continue until completion). + - RESUME to reactivate the campaign. + If the campaign has already ended, the API will respond with a 400 error, indicating that the campaign is finished and cannot be modified. Pausing a campaign does not extend its end date or overall duration. + operationId: manageCampaign + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + requestBody: + description: Parameters to manage the campaign. + required: true + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + action: + type: string + enum: + - pause + - resume + description: "The action to be performed on the campaign. It can be 'PAUSE' to pause or 'RESUME' to resume." + responses: + '200': + description: Successful operation + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + requestResult: + type: string + example: "CAMPAIGN PAUSED SUCCESSFULLY or CAMPAIGN RESUMED SUCCESSFULLY" + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + startTime: + $ref: "#/components/schemas/Time" + status: + type: string + description: Current status of the campaign (e.g., "active", "paused", "completed"). + enum: + - paused + - resumed + - completed + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + +components: + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation identifier in UUID version 4 format + required: true + schema: + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" # UUID versión 4 regular expression + x-accessToken: + name: accessToken + in: header + description: Access token for the Sponsor. + required: true + schema: + type: string + x-callbackToken: + name: x-callbackToken + in: header + description: | + Security token for authenticating the notification. It must match the value provided in the callbackToken field of the initial sponsorship request body. + required: true + schema: + type: string + format: uri + example: https://tonys-server.com + headers: + x-correlator: + description: | + A unique identifier used to correlate requests and responses across the API. + Useful for tracing, debugging, and ensuring consistency between sponsor operations and system events. + required: true + schema: + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" + schemas: + SponsorId: + type: string + description: Unique sponsor identifier, assigned by the API GW Platform operator. Should include a domain associated with the company for easy recognition. + pattern: "^[a-zA-Z0-9._%+-]+@[a-zA-Z0-9.-]+\\.[a-zA-Z]{2,}$" # Excample 'ID@sponsor_domain.com' + CampaignId: + type: string + description: Unique identifier for the campaign, including a UUID and the sponsor's domain. + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12}@[a-zA-Z0-9.-]+\\.[a-zA-Z]{2,}$" # Example "UUID@sponsor_domain.com" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + SessionId: + description: Unique session identifier, assigned by the API GW Platform operator. Should include a domain associated with the company for easy recognition. + type: string + format: uuid + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12}$" + CampaignNotification: + description: | + Provides details about a campaign-related event or alert, such as nearing data limits, expiration of the campaign, or other operational notifications. Intended to keep sponsors informed about relevant changes or milestones in their campaigns. + type: object + properties: + api_version: + description: Data Sponsored API Version (must be 1.0.0) + type: string + enum: + - '1.0.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + type: string + description: Identificador de la campaña. + eventType: + type: string + description: Tipo de evento que desencadenó la notificación. + enum: + - DATA_VOLUME_THRESHOLD_EXCEEDED (80%) + - DATA_VOLUME_EXHASTED + - CAMPAIGN_EXPIRED + timestamp: + type: string + format: date-time + description: Fecha y hora en que ocurrió el evento. + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + WebhookUrl: + type: string + format: url + description: The URL to which notifications about session status changes will be sent using the HTTP protocol. (e.g., session termination) + example: "https://sponsor.endpoint.example.com/webhook" + SponsorshipEndNotification: + description: > + Contains information about the conclusion of a sponsored data session for a user. + Includes the reason for ending the sponsorship, session identifiers, and relevant timestamps, allowing sponsors to track session completion and handle post-sponsorship actions. + type: object + properties: + api_version: + description: Data Sponsored API Version (must be 1.0.0) + type: string + enum: + - '1.0.0' + datacontenttype: + description: media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs + type: string + enum: + - 'application/json' + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + reason: + type: string + description: Reason for the termination of the sponsorship. + enum: + - EXPIRED + - TERMINATED_BY_SPONSOR + - DATA_EXHAUSTED + - USER_DEREGISTERED + - NOT_AVAILABLE + endTimestamp: + type: string + format: date-time + description: Date and time when the sponsorship session ended. + Time: + description: | + Exact time in ISO 8601 format. + 1) Date and time when the sponsorship started or when the session expires if it is still active, + 2) End date and time of the sponsorship. Calculated by adding the specified sponsorship duration to the start time (startTime).If duration is not specified, the default value defined in the onboarding campaign profile is used. + 3) End time if the session concluded due to data volume exhaustion, + 4) or when the sponsorship finished, + 5) or when the campaign started, + 6) or when the campaign expires if it is still active, + 7) or the end time if the campaign concluded due to data volume exhaustion, + 8) or when the requested action (PAUSE or RESUME) on the campaign takes effect. + 9) Start and endtime in revoke operation referes to the sponsored session revoked + type: string + format: date-time + example: "2024-08-20T14:34:56Z" + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: | + Client does not have sufficient permission. + In addition to regular scenario of `PERMISSION_DENIED`, other scenarios may exist: + - Phone number cannot be deducted from access token context.(`{"code": "INVALID_TOKEN_CONTEXT","message": "Phone number cannot be deducted from access token context"}`) + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + NOT_FOUND: + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found + DEVICE_IDENTIFIER_NOT_FOUND: + value: + status: 404 + code: DEVICE_NOT_FOUND + message: Some identifier cannot be matched to a device + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by the client through `Accept-*` headers. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic415: + description: Unsupported Media Type + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Payload format of the request is in an unsupported format by the Server. Should not happen + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Generic422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_422_DEVICE_IDENTIFIERS_MISMATCH: + description: Inconsistency between device identifiers not pointing to the same device + value: + status: 422 + code: DEVICE_IDENTIFIERS_MISMATCH + message: Provided device identifiers are not consistent. + GENERIC_422_DEVICE_NOT_APPLICABLE: + description: Service is not available for the provided device + value: + status: 422 + code: DEVICE_NOT_APPLICABLE + message: The service is not available for the provided device. + GENERIC_422_UNABLE_TO_PROVIDE_REACHABILITY_STATUS: + value: + status: 422 + code: UNABLE_TO_PROVIDE_REACHABILITY_STATUS + message: Network issue - Unable to provide reachability status + GENERIC_422_UNSUPPORTED_DEVICE_IDENTIFIERS: + value: + status: 422 + code: UNSUPPORTED_DEVICE_IDENTIFIERS + message: None of the provided device identifiers is supported by the implementation + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as far as possible to get the objective to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. +``` diff --git a/marked/SponsoredData/documentation/API_documentation/README/raw.md b/marked/SponsoredData/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SponsoredData/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SponsoredData/documentation/MeetingMinutes/README/raw.md b/marked/SponsoredData/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8b137891791fe96927ad78e64b0aad7bded08bdc --- /dev/null +++ b/marked/SponsoredData/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1 @@ + diff --git a/marked/SponsoredData/documentation/SupportingDocuments/Presentations/README/raw.md b/marked/SponsoredData/documentation/SupportingDocuments/Presentations/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8b137891791fe96927ad78e64b0aad7bded08bdc --- /dev/null +++ b/marked/SponsoredData/documentation/SupportingDocuments/Presentations/README/raw.md @@ -0,0 +1 @@ + diff --git a/marked/SponsoredData/documentation/SupportingDocuments/README/raw.md b/marked/SponsoredData/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SponsoredData/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/SubscriptionStatus/README/raw.md b/marked/SubscriptionStatus/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..70259b3f2154bd8ed0a02b5c809e117ad89a3b20 --- /dev/null +++ b/marked/SubscriptionStatus/README/raw.md @@ -0,0 +1,51 @@ + + + + + + + + + +# SubscriptionStatus + +Sandbox API Repository to describe, develop, document, and test the SubscriptionStatus Service API within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/hACbBQ) + +## Scope + +* Service API “SubscriptionStatus” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the customer with the ability to: + * obtain the current subscription status of a certain phone number, including the subscription of Voice/SMS Inbound, Voice/SMS Outbound, and Data Service Status +* Describe, develop, document, and test the APIs +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/SubscriptionStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **subscription-status v0.1.0** + [[YAML]](https://github.com/camaraproject/SubscriptionStatus/blob/r1.2/code/API_definitions/subscription-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SubscriptionStatus/r1.2/code/API_definitions/subscription-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SubscriptionStatus/r1.2/code/API_definitions/subscription-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SubscriptionStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SubscriptionStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SubscriptionStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of Sub Project KnowYourCustomer are held virtually + * Schedule: Bi-weekly, Tuesday, 09:00 CEST (07:00 UTC) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/FAje) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/SubscriptionStatus/code/API_definitions/subscription-status/raw.md b/marked/SubscriptionStatus/code/API_definitions/subscription-status/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..55cad7653d38c71af5d265f7e03d9a5ade3d4f9d --- /dev/null +++ b/marked/SubscriptionStatus/code/API_definitions/subscription-status/raw.md @@ -0,0 +1,355 @@ +# subscription-status + +```yaml +openapi: 3.0.3 +info: + title: SubscriptionStatus + description: | + This API allows users to obtain the current subscription status of a phone number, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + + # Introduction + + This API obtains the business subscription status of a phone number by passing it in, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + + Normally, the business subscription status is active, and the following situations may lead to abnormal business subscription status. + + **Overdue fees and downtime**: If the account balance is insufficient or the monthly rental fee is not paid on time, the operator may suspend the service. + + **Real name authentication issue**: If identity information is not updated in a timely manner (such as expired documents or incomplete second real name authentication), the operator may freeze the account. + + **Violation**: Frequent making harassing phone calls, engaging in illegal activities, and other behaviors can lead to service suspension. + + **Abnormal usage behavior**: High frequency outgoing calls, long-distance roaming, sensitive period communication, and other behaviors may be detected by the operator's risk control system, which may lead to service suspension. + + It helps verify whether telecommunication services are active or suspended for fraud prevention, customer support, and operational checks. + + **Scenario 1 - Payment System Validation**: + * A financial service provider uses this API to validate if a user's phone number has active voice/SMS services before processing high-risk transactions. If the API returns "suspended" for Voice/SMS inbound, the transaction is flagged for manual review to prevent fraud or invalid transfers. + + **Scenario 2 - Customer Service Troubleshooting**: + * The user reported that they were unable to receive calls. Customer support queries the API and identifies that "Voice/SMS inbound" is suspended. + * The user reported that they were unable to make a phone call. Customer support queries API and confirms that 'voice/SMS outbound' is suspended + * The user reported that they are unable to use the data service.Customer support queries API and confirms that 'data service status' is suspended + + The customer service personnel guides the user to reactivate the service, resolving the issue. + + # Relevant terms and definitions + - **Voice/SMS Inbound** + Indicates the ability of the subscriber to **receive** incoming voice calls and SMS messages. + - `active`: The subscriber can receive calls and SMS normally. + - `suspended`: The subscriber is blocked from receiving calls/SMS (e.g., due to account suspension). + + - **Voice/SMS Outbound** + Indicates the ability of the subscriber to **initiate** outgoing voice calls and send SMS messages. + - `active`: The subscriber can make calls and send SMS normally. + - `suspended`: The subscriber is blocked from initiating calls/SMS (e.g., due to unpaid bills or fraud restrictions). + + - **Data Service Status** + Indicates the availability and performance level of mobile data connectivity. + - `active`: Full-speed data access is enabled. + - `suspended`: Data service is completely disabled (e.g., due to contract expiration). + - `throttled`: Data service is available but speed is reduced (e.g., after exceeding usage limits). + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + version: 0.1.0 + + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/SubscriptionStatus +servers: + - url: "{apiRoot}/subscription-status/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root defined by the provider (e.g., `api.example.com`). + +paths: + /retrive-subscription-status: + post: + security: + - openId: + - subscription-status:retrive-subscription-status + tags: + - Retrive Subscription Status + description: | + Obtain the business subscription status of the provided phone number, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + operationId: retriveSubscriptionStatus + summary: Retrieve subscription status of a phone number + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionStatusRequest" + examples: + Three-Legged Without Phone Number Example: + value: {} + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: "+346661113334" + responses: + "200": + description: Subscription status retrieved successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionStatusResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for cross-service tracking + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SubscriptionStatusRequest: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + SubscriptionStatusResponse: + type: object + required: + - voiceSmsIn + - voiceSmsOut + - dataService + properties: + voiceSmsIn: + type: string + enum: [active, suspended] + description: Status of inbound Voice/SMS services + voiceSmsOut: + type: string + enum: [active, suspended] + description: Status of outbound Voice/SMS services + dataService: + type: string + enum: [active, suspended, throttled] + description: Status of mobile data service + PhoneNumber: + type: string + pattern: "^\\+[1-9][0-9]{4,14}$" + example: "+8613800138000" + description: E.164 formatted phone number + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token +``` diff --git a/marked/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist/raw.md b/marked/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..75ea2b7edb5a741c0c1140dd7c3a757ebc955fce --- /dev/null +++ b/marked/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for subscription-status v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/subscription-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/subscription-status.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/subscription-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/subscription-status.feature) | +| 9 | Test result statement | O | O | O | M | N | To be provided | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/hACbBQ) | diff --git a/marked/SubscriptionStatus/documentation/SupportingDocuments/README/raw.md b/marked/SubscriptionStatus/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/SubscriptionStatus/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/Tenure/README/raw.md b/marked/Tenure/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f63a122ae744e98298d135759bafd1034e66b3e0 --- /dev/null +++ b/marked/Tenure/README/raw.md @@ -0,0 +1,47 @@ + + + + + + + + + +# Tenure + +Sandbox API Repository to describe, develop, document, and test the Tenure Service API(s) within the Sub Project [Know Your Customer (KYC)](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ZIDGB) + +## Scope +* Service API(s) for “Tenure” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + * Establish a level of trust for a given network subscription identifier (e.g. phone number) by verifying the period of time (i.e. "tenure") for which the end user currently allocated that identifier has been associated with it by their current network operator. +* Describe, develop, document, and test the APIs +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/Tenure/releases/tag/r2.2) (Fall25), with the following API versions: + * **kyc-tenure v0.2.0** + [[YAML]](https://github.com/camaraproject/Tenure/blob/r2.2/code/API_definitions/kyc-tenure.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/Tenure/r2.2/code/API_definitions/kyc-tenure.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/Tenure/r2.2/code/API_definitions/kyc-tenure.yaml) +* The latest public release is always available here: https://github.com/camaraproject/Tenure/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/Tenure/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/Tenure/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings and minutes see [KnowYourCustomer Meetings](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-kyc + * A message to the community of this Sub Project can be sent using diff --git a/marked/Tenure/code/API_definitions/kyc-tenure/raw.md b/marked/Tenure/code/API_definitions/kyc-tenure/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..fe4770a1702f91650a6da3db733cec8deba7cc45 --- /dev/null +++ b/marked/Tenure/code/API_definitions/kyc-tenure/raw.md @@ -0,0 +1,392 @@ +# kyc-tenure + +```yaml +openapi: 3.0.3 +info: + title: KYC Tenure + description: | + # Summary + + The CAMARA Know Your Customer (KYC) Tenure API allows for verification that a network subscriber has been a customer of the Communications Service Provider (CSP) for a specified minimum length of time so as to establish a level of trust for the associated network subscription identifier. + + # API functionality + + The API defines one service endpoint: + + - `POST /check-tenure` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and the specified minimum tenure date to validate for the associated network subscription. This endpoint will respond with a confirmation of whether or not the network subscriber tenure is longer than the specified date timestamp, optionally supplemented with details of the subscription contract type. + + To call this endpoint, the API consumer must first obtain a valid access token with the specified scope from the specified token endpoint, which is then passed to the endpoint via the `Authorization` header. For more details on access token processing, see below. + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `tenureDate`: The date from which continuous tenure of the identified network subscriber is required to be confirmed. This field is always required. + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). This field is only required if no network subscription identifier is associated with the access token. + + Note: MNOs may implement a threshold for the tenureDate aligned with their respective regulations. In that case if the tenureDate value in the request body is over the operator's threshold an error `400 OUT_OF_RANGE `is returned with an explicit message to explain the limitation. + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `tenureDateCheck`: `true` when the identified network subscription has had valid tenure since `tenureDate`, otherwise `false` + - `contractType`: The network subscription account type, if known + + An example of a JSON response object is as follows: + ``` + { + "tenureDateCheck": true, + "contractType": "PAYM" + } + ``` + + ## Errors + + If the authentication token is missing, not a valid token, or is no longer valid, a `401 UNAUTHENTICATED` error is returned + + If the API call contain a formatting or other error, a `400 INVALID_ARGUMENT` error is returned. + + If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + + If the API consumer has a valid access token that does not have the required scope to obtain tenure information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/Tenure + +servers: + - url: "{apiRoot}/kyc-tenure/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: API root + +tags: + - name: Check Subscriber Tenure + description: Check details about the length of tenure of the subscriber + +paths: + /check-tenure: + post: + tags: + - Check Subscriber Tenure + summary: The KYC Tenure service API + description: | + Verifies a specified length of tenure, based on a provided date, for a network subscriber to establish a level of trust for the network subscription identifier. + + security: + - openId: + - kyc-tenure:check-tenure + + operationId: checkTenure + + parameters: + - in: header + name: x-correlator + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/Tenure" + + responses: + "200": + description: Respond with tenure information + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/TenureInfo" + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token + + + schemas: + Tenure: + description: Specifies date from which continuous tenure of the identified mobile subscriber is required to be confirmed + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + tenureDate: + type: string + description: The date, in RFC 3339 / ISO 8601 compliant format "YYYY-MM-DD", from which continuous tenure of the identified network subscriber is required to be confirmed + format: date + example: "2023-07-03" + required: + - tenureDate + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + TenureInfo: + properties: + tenureDateCheck: + description: | + `true` when the identified mobile subscription has had valid tenure since `tenureDate`, otherwise `false` + example: true + type: boolean + contractType: + description: | + If exists, populated with: + - `PAYG` - prepaid (pay-as-you-go) account + - `PAYM` - contract account + - `Business` - Business (enterprise) account + + This attribute may be omitted from the response set if the information is not available + example: "PAYM" + type: string + enum: ["PAYG", "PAYM", "Business"] + required: + - tenureDateCheck + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" +``` diff --git a/marked/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist/raw.md b/marked/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..588ed8f83b0a086780d7c8591170a27c7f7df720 --- /dev/null +++ b/marked/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for kyc-tenure v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](/code/API_definitions/kyc-tenure.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Documentation embedded within [API definition](/code/API_definitions/kyc-tenure.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/kyc-tenure.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/wAPWB) | diff --git a/marked/Tenure/documentation/SupportingDocuments/README/raw.md b/marked/Tenure/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/Tenure/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/TrafficInfluence/README/raw.md b/marked/TrafficInfluence/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..782433f158b7773682c856a02b32246462f4b7b5 --- /dev/null +++ b/marked/TrafficInfluence/README/raw.md @@ -0,0 +1,53 @@ + + + + + + + + + +# TrafficInfluence + +Sandbox API Repository to describe, develop, document, and test the TrafficInfluence Service API(s) within the Sub Project [EdgeCloud](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XQCbBQ) + +## Scope + +* Service API(s) “TrafficInfluence” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Influence the traffic flow from the user device toward the Edge instance of the Application providing the optimal routing. + * The traffic can be influencend even when the user device moves to a different geographical location to always get the optimal routing toward the nearer instance of an Application. +* Describe, develop, document, and test the API(s) +* Started: February 2025 (with previous work in EdgeCloud repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/TrafficInfluence/releases/tag/r1.3) (Fall25), with the following API versions: + * **traffic-influence v0.10.0** + [[YAML]](https://github.com/camaraproject/TrafficInfluence/blob/r1.3/code/API_definitions/traffic-influence.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/TrafficInfluence/r1.3/code/API_definitions/traffic-influence.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/TrafficInfluence/r1.3/code/API_definitions/traffic-influence.yaml) +* The latest public release is always available here: https://github.com/camaraproject/TrafficInfluence/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/TrafficInfluence/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/TrafficInfluence/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of the EdgeCloud Sub Project are held virtually + * Schedule: Tuesdays 1400-1500 UTC, every two weeks (see [CAMARA Community Calendar](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) for concrete dates) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/TrafficInfluence/code/API_definitions/traffic-influence/raw.md b/marked/TrafficInfluence/code/API_definitions/traffic-influence/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..db53410fe50ea8b0a944e9d202904c006612b539 --- /dev/null +++ b/marked/TrafficInfluence/code/API_definitions/traffic-influence/raw.md @@ -0,0 +1,1580 @@ +# traffic-influence + +```yaml +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Traffic Influence + description: | + # Overview + The reference scenario foresees a Service, composed by one or more Service + Producers deployed in different geographical locations in a distributed + Telco Edge Cloud. The Service Producer, deployed at the Edge, is referred + as Edge Application Server. + + The life cycle management of the Edge Application Server can be done with APIs, for example the CAMARA + "Edge Application Management API" under definition in the CAMARA Edge + Cloud repository (https://github.com/camaraproject/EdgeCloud). + The Telco Edge Cloud is composed by Edge Cloud Regions that contain + Edge Cloud Zones. For a more complete definition of such Telco Edge Cloud + architecture, please refer to the "Edge Application Management API" + documentation. A developer can deploy and run applications on an Edge + Cloud Zone, meaning reduced latency to end users that are nearby, as the + network path is shorter. A network operator's EdgeCloud may comprise + multiple Edge Cloud Zones, each in a discrete location to bring latency + benefits to end users across a country. + + The operator can help developers knowing which of the Edge Cloud Zones will + bring the optimal performance for a given end user and application. + + The Traffic Influence API provides the optimal routing from the + user Device (e.g. a Smartphone) to the optimal Edge Application Server instance in a specific + geographical location, installed in an Edge Cloud Zone. + + If a Service is offered by Cloud Instances and by Edge Instances, the Traffic Influence + API can be used get the optimal routing of the traffic to the Edge + Instances, maybe for a set of users. Getting the optimal routing can be + used to improve latency maybe in combination with other CAMARA APIs such as + QoD (Quality On Demand). Providing the optimal routing is indeed an + important step to get the optimal latency. + + If the Traffic Influence API is used to get the best routing at the Edge for a Device in a + geographical location and the Device moves to another geographical location, + the Traffic Influence API can be invoked to get the optimal routing in the new geographical + location for that Device. + + While the goal of the Traffic Influence API is to optimise the traffic in the mobile + network to reach the local instance of the Edge Application Server, it is a task of the + Application to generate the flow toward the expected Edge Application Server Instance. + # Introduction + The Traffic Influence API provides the capability to establish the optimal routing, in + terms of latency, in a specific geographical area, between the user Device, + e.g. the user’s smartphone, and the optimal Edge Application Server instance nearby. If the + Device moves in a different geographical location where a more suitable Edge Application Server + instance is available, the Traffic Influence API can be invoked again to influence the + Device connectivity to get the optimal routing also in the new location. + It is important to notice that the service data flow is not automatically + optimised when the user moves in a specific area, it is a task of the Traffic Influence API + Consumer to detect the changes in the Device location and to invoke the + Traffic Influence API consequently. + + The generic architecture for the Service can foresee some Cloud instances of + the Application, one or more Edge Instances of the Application. The Traffic Influence API + Consumer invokes the Traffic Influence API creating a "TrafficInfluence" resource + specifying the desired intent. + + The Traffic Influence API Producer implements the intent specified in the + "TrafficInfluence" resource. + + While the Traffic Influence API can be invoked to activate the optimal routing for any + user, it can also be used to request the optimal routing for a specific user + also specifying, as an option, a source public port and a destination public + port and protocol. Invoking the Traffic Influence API for each user, many + "TrafficInfluence" resources are created for each user to provide the + requested routing for a set of users. If the Traffic Influence API is invoked to provide + the optimal routing for any user and later it is required to provide the + optimal access only for selected users, the previous intent/resource must + be deleted. + + The same approach is used for the geographical areas where the influence + of the traffic must be applied. Invoking the Traffic Influence API without specifying a + geographical area, activates the optimal routing toward the closest Edge Application Server + instance in any geographical location. This intent must be deleted if it is + required to provide the optimal access only in selected areas. Invoking the + Traffic Influence API specifying a geographical area activates the optimal routing only if + the user is in that geographical area. The flow is optimised to reach the + Edge Application Server instance located closest to that geographical area. In a different + geographical area the user will not have the traffic flow optimised. + + To activate the optimal routing in selected geographical areas, the Traffic Influence API + must be invoked for each geographical area. Anyway it is important to + understand that the traffic optimisation strongly depends on the user's + geographical location so it is important for the Traffic Influence API Consumer to always + verify the position of the user invoking the Traffic Influence API for that user if it + moves changing its location. + The API API can also be used to optimise a specific traffic flow identified + by a source port and a destination port and protocol. To optimise the flow + from more source ports or destination ports or protocols, the Traffic Influence API must be + invoked many times. + + It is important to notice that it is a task of the Client Application to + use the most adequate means to send the application flow to the right + server (Edge Application Server), for example using Edge DNS or using the target Edge Application Server IP address. + The Traffic Influence API provides back the selected Edge Application Server instance identifier from which the + Client Application can retrieve the destination IP address of its backed + server, to properly configure the service data flow. + + The Traffic Influence API can be used to: + - optimise the routing when Devices need to consume the service provided + by a local Edge Application Server Instances. + - affect an already established Device routing when the Device moves + among different geographical locations. When the Traffic Influence API consumer detects + a Device has entered a geographical location where an Edge Application Server instance is + available, it can invoke the Traffic Influence API to get the optimal routing toward + that Edge Application Server instance. + If the Device moves to another geographical location, served by another + Edge Application Server instance, the routing might not be optimal any more. In the case the + Application detects a location change, it can invoke the Traffic Influence API again to + request a new routing optimization toward the new Edge Application Server instance. + ## Quick Start + The Traffic Influence API is consumed by an Application Function (AF) requesting for the + optimal routing, in term of latency, for the traffic flow from a Device + toward Edge Application Server instances in Edge Cloud Zones. + + When the Application (the Edge Application Server) is onboarded and deployed in the Edge Cloud + Zones, the Application is identified with a unique identifier ("appId"). + + Using the application identifier ("appId") and specifying a Zone or a Region + the Telco Operator Platform, autonomously identifies the best instance of + the Edge Application Server toward which routing the traffic flow and configures the Mobile + Network accordingly to get the fastest routing. + + If just the application identifier is used, the Telco Operator Platform + identifies all the Edge Application Server Instances and activates the optimal routing on the + Mobile Network. + + If the optimal routing in term of latency should be available just for a set + of users, the Traffic Influence API must be invoked for each user creating a new + TrafficInfluce resource for each one. + If the Application offers different services on different interfaces a + traffic filter based on IP, Port and Protocol can be used. I this way it is + also possible to redirect different users to different interfaces. + Here are some possible intents: + 1) activate the optimal routing for the closest Edge Application Server instance: the Traffic Influence API + must be invoked with the "appId". The Telco Operator Platform identifies + all the Edge Application Server instances and activates the optimal routing on the Mobile + Network so that the user is connect to the closest Edge Application Server instance. + 2) activate the optimal routing in a specific Region or Zone: the Traffic Influence API + must be invoked with the "appId" and the Zones and Regions identifiers. + 3) activate the optimal routing for a user Device: the Traffic Influence API can be + invoked with a user Device identifier (“Device”). For each user Device, + a Traffic Influence API invocation is required. The optimal routing is provided only for + the requested Devices. + # API Documentation + The usage of the Traffic Influence API is based on the management of a "TrafficInfluence" + resource, an object containing the intent requested invoking the Traffic Influence API and + that is implemented by the platform configuring the Mobile Network for the + optimal routing toward the Edge Application Server instance. + + The "TrafficInfluence" resource can be created (providing the related + parameters that specify the desired intent), queried, modified and + deleted. + + The Traffic Influence API is asynchronous, a notification is available providing + information about the status of the requested resource. + For an Application (identified by "appId") many "TrafficInfluence" resources + can be created, e.g. to add multiple users, regions or zones. + + When an intent is expressed and a resource have been created, if the intent + must be modified, it is suggested to use the PATCH method + (/traffic-influeces/{trafficInfluenceID}). Anyway, any other new intent + (e.g. for the same device) will override the previous ones. + + Before starting to use the Traffic Influence API, the developer needs to know about the + below specified details: + + **TrafficInfluence:** + This object represents the resource that carries the requirements from the + user to be implemented. The Traffic Influence API is invoked for the life cycle management + of this resource (CRUD). The resource contains the intents from the Traffic Influence API + Consumer. Managing this resource, the developer can specify in which + geographical location the routing must be applied, toward which application, + maybe for a specific set of users or for a limited period of time. + + **trafficInfluenceID:** + Identifier for the Traffic Influence resource. This parameter is returned + by the Traffic Influence API and must be used to update it (e.g., adding a Device or + deleting it). A different Traffic Influence resource must be created for + any Device or Zone or Region. All these resources are related to an + Application identified by "appId". + + **apiConsumerId:** + Unique identifier for the Traffic Influence API Consumer. + + **edgeCloudRegion:** + The Developer can specify in which geographical area he requires the optimal + routing toward application instances running there. An Edge Cloud Region is + equivalent to a Region on a Public Cloud. The higher construct in the + hierarchy exposed to an Application Provider who wishes to deploy an + Application on the Edge Cloud and broadly represents a geography. + An Edge Cloud Region typically contains one or multiple Edge Cloud Zones. + The Edge Cloud Region name is provided by the Telco Operator and can also be + used or retrieved with other CAMARA APIs (e.g. “Edge Application Management + API”). To add more regions the Traffic Influence API must be invoked (POST) for each + "region". If in a "region" there are many Application instances active in + different "zones", the Traffic Influence API can be invoked to configure the optimal + routing for all the instances with just one API call specifying the + "region". + + If just the Application instances in some Edge Cloud Zone must be affected, + the Traffic Influence API can be invoked for the zones of interest, without specifying + the "region" in the API call. If just some specific Application instance + must be affected, it is not required to specify any "region" or "zone", + and the parameter "appInstanceId" can be used. + + **edgeCloudZoneId:** + An Edge Cloud Zone is the lowest level of abstraction exposed to an + Application Provider who wants to deploy an Application on Edge Cloud. + Edge Cloud Zones exists within a Edge Cloud Region. + + To add more "zones" the Traffic Influence API must be invoked (POST) for each "zone". + + **appId:** + A globally unique identifier associated with the application. This + identifier is provided during the application onboarding process. + To influence the traffic toward a specific Application. It is the Operator + Platform that detects the appropriate Application instance in the selected + "region" or "zone". + + **appInstanceId:** + A globally unique identifier generated by the Operator Platform to identify + a specific instance of the Application in a specific zone. To influence a + traffic toward a specific Application instance. If just some specific + Application instance must be affected, it is not required to specify any + "region" or "zone", the parameter "appInstanceId" can be used. + The value for appInstanceId can be retrieved using the CAMARA API + Edge Application Management, included in the Edge Cloud API Family. + + **sourceTrafficFilters:** + The traffic can be from a specific public port in the device. If this + parameter is used, the influenced flow is from the public port defined in + "sourceTrafficFilters" rather than the public port specified in "Device" + + **destinationTrafficFilters:** + The Application can expose different service on different interfaces, + identified by port and protocol, with this parameter it is possible to + route the traffic toward a specific port and protocol exposed by the + Application. + + **Device:** + An user Device can be provided as an input. The Device can be identified by + the phone number (phoneNumber) or by its IP Address (Ipv4Address, + Ipv6Address) also specifying a Port. For IP address both the private (as + seen from inside the Device) and the public (as seen over Internet by a + server connected to the Device) can be used. To add more users the Traffic Influence API + must be invoked (POST) of each user Device. New "TrafficInfluence" + resources are created (with different "trafficInfluenceID"). The routing + toward the selected Application instance is only applied for provided user + Devices. "publicPort" can be used to identify the device. "publicPort" can + be also used to identify the flow to be influenced. If the flow to be + influenced is from a different public port, "sourceTrafficFilters" can be + used. If more than one Device identifier is provided only one will be used + by the Traffic Influence API to perform the network optimization. The one used is + returned in the notification callback. + + **Notification:** + Developers can specify a callback URL on which notifications + regarding the requested intent can be received. The notification will be + sent as a CloudEvent compliant message. For example to be notified when the + requested optimal routing is active. It is also provided back the + identifier for the selected Edge Application Server instance ("selected_appInstanceId") + from which the Client Application can retrieve the destination IP address of + its back-end server, to properly configure the service data flow. This + information can be retrieved using the APIs, for example the Edge Application Management under development in CAMARA. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during + the onboarding process, happening between the provider of the application + consuming the API and the operator's API exposure platform, taking into + account the declared purpose for accessing the API, whilst also being + subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Identifying the phone number from the access token + This API optionally requires the API consumer to identify a phone number + as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject + will be identified from the optional `device` object field, which + therefore MUST be provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a + three-legged access token to invoke the API by relying on the + information that is associated with the access token and was + identified during the authentication process. + ## Error handling: + - If the subject cannot be identified from the access token and the + optional `device` object field is not included in the request, then + the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the + optional `device` object field is also included in the request, then + the server will return an error with the `422 UNNECESSARY_IDENTIFIER` + error code. This will be the case even if the same device is + identified by these two methods, as the server is unable to make + this comparison. + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + # FAQ's + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/TrafficInfluence +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/traffic-influence/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root for the Traffic Influence API +############################################################################ +# Tags # +############################################################################ +tags: + - name: Traffic Influence API read + description: Reads existing TrafficInfluence resources + - name: Traffic Influence API write + description: Creates of modifies a TrafficInfluence resource +############################################################################ +# Paths # +############################################################################ +paths: + /traffic-influences: + get: + security: + - openId: + - 'traffic-influence:traffic-influences:read' + parameters: + - $ref: '#/components/parameters/x-correlator' + - in: query + name: appId + schema: + $ref: "#/components/schemas/AppId" + description: Used to select traffic influence resources filtered by + appId. For privacy reasons, if a resource is related to a user, the + parameter Device is not returned. + tags: + - Traffic Influence API read + summary: Retries existing TrafficInfluence Resources + description: Reads all of the active TrafficInfluence resources owned by + the same API Consumer + operationId: getAllTrafficInfluences + responses: + '200': + description: Returns the information about existing TrafficInfluence + resources. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/TrafficInfluence" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + post: + tags: + - Traffic Influence API write + summary: Creates a new TrafficInfluence resource influencing the + traffic toward local instances of the Application for any user. + description: Takes as input an object containing the intents from the API + Consumer and creates a TrafficInfluence resource accordingly. The + trafficInfluenceID parameter, that is part of the object, must not be + valorized when creating a new resource. For this reason the + trafficInfluenceID parameter must be avoided in the object, anyway it + will be ignored by the API Producer. It is automatically generated by + the system and returned in the response. + operationId: postTrafficInfluence + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:write' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PostTrafficInfluence' + responses: + '201': + description: TrafficInfluence resource created, the related object is + returned with the resource ID (trafficInfluenceID) and status (state) + valorised. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "409": + $ref: "#/components/responses/Generic409" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + /traffic-influence-devices: + post: + tags: + - Traffic Influence API write + summary: Creates a new TrafficInfluence resource influencing the + traffic toward local instances of the Application for a specific user. + description: Takes as input an object containing the intents from the API + Consumer and creates a TrafficInfluence resource accordingly. The + trafficInfluenceID parameter, that is part of the object, must not be + valorized when creating a new resource. For this reason the + trafficInfluenceID parameter must be avoided in the object, anyway it + will be ignored by the API Producer. It is automatically generated by + the system and returned in the response. + operationId: postTrafficInfluenceDevice + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influence-devices:write' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PostTrafficInfluenceDevice' + responses: + '201': + description: TrafficInfluence resource created, the related object is + returned with the resource ID (trafficInfluenceID) and status (state) + valorised. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + /traffic-influences/{trafficInfluenceID}: + parameters: + - name: trafficInfluenceID + in: path + description: Identifier of the specific TrafficInfluence resource to be + retrieved, modified or deleted. It is the value used to fill + trafficInfluenceID parameter. + required: true + schema: + type: string + get: + tags: + - Traffic Influence API read + summary: Reads a specific TrafficInfluence resource identified by the + trafficInfluenceID value. + description: Returns a specific TrafficInfluence resources owned by the + same API Consumer. For privacy reasons, if a resource is related to a + user, the parameter Device is not exchanged. + operationId: getTrafficInfluenceById + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:read' + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + patch: + tags: + - Traffic Influence API write + summary: updates a specific TrafficInfluence resource, identified by the + trafficInfluenceID value. If used for a specific user, the Device + parameter can not be modified. + description: The resource identified by the trafficInfluenceID value can + be modified. Before the PATCH can be invoked the status (state) of the + resource must be "active". If not an error code 409 (DENIED_WAIT) is + returned. + operationId: patchTrafficInfluence + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:update' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PatchTrafficInfluence' + responses: + '200': + description: TrafficInfluence resource edited, the related object is + returned, the status (state) is updated. + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + headers: + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + delete: + tags: + - Traffic Influence API write + summary: Delete an existing TrafficInfluence resource + description: invoked by the API Consumer to stop influencing the traffic, + deleting a TrafficInfluence resource previously created. The notification + will be sent via Cloud Event with the information already available in + the TrafficInfluence resource identified by "trafficInfluenceID". + operationId: deleteTrafficInfluence + security: + - openId: + - 'traffic-influence:traffic-influences:delete' + parameters: + - $ref: '#/components/parameters/x-correlator' + responses: + '202': + description: Deletion in progress. + resources. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + description: to support both Consent Management, via 3-legged authentication, + when sensitive data are exchanged and OAuth2, 2-legged authentication, + for endpoints not exchanging sensitive data. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onTrafficInfluenceChanged: + # when data is sent, it will be sent to the callback url provided + '{$request.body.subscriptionRequest.sink}': + post: + tags: + - Traffic Influence CALLBACK Operation + summary: Provides a notifican channel for changes in the + TrafficInfluence resource + description: Creating, modifying or delating a Traffic Influece + resourece is an asycronous task. For this reason a notification + channel via callback to a specified URL is provided. + operationId: trafficInfluenceCloudEvent + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: subscription payload which contains the updated + traffic influence instance + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + datacontenttype: "application/json" + type: "org.camaraproject.traffic-influence.v1.traffic-influence-change" + data: + selected_appInstanceId: + - "3fa85f64-5717-4562-b3fc-2c963f66afa6" + deviceResponse: + phoneNumber: "+123456789" + time: "2018-04-05T17:31:00Z" + responses: + '202': + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '204': + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '401': + description: Your server should return this HTTP status code if + the request can not be authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + ########################################################################## + # Resources # + ########################################################################## + schemas: + TrafficInfluence: + description: Resource conteining the informations to influence the + traffic toward local instances of the Application, for any user. + type: object + properties: + trafficInfluenceID: + type: string + description: Identifier for the Traffic Influence resource. This + parameter is returned by the API and it is used to update it + (e.g., modify or delete the TrafficInfluence resource). + apiConsumerId: + type: string + description: Unique Identifier of the Traffic Influence API Consumer. + appId: + $ref: '#/components/schemas/AppId' + appInstanceId: + $ref: '#/components/schemas/AppInstanceId' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + state: + type: string + description: it reports the state of the TrafficInfluence resource. + When first invoked, the resource is 'ordered'. When the platforms + prepares the resource, it is 'created'. When the new routing is + enabled in the network, the state is 'active'. If an error occurs + in the resource creation or in its activation, the state is 'error'. + When the DELETE method is invoked the state is + 'deletion in progress'. + After the resource is deleted (as a consequence of the previous + invocation of the DELETE method) the state is 'deleted'. + enum: + - 'ordered' + - 'created' + - 'active' + - 'error' + - 'deletion in progress' + - 'deleted' + sourceTrafficFilters: + description: Public source port used by the device for flows to which + the requested traffic influence should apply. Traffic influence will + be applied to the flow between "sourcePort" and the Application + Server address and port specified in "destinationTrafficFilters". + type: object + properties: + sourcePort: + allOf: + - $ref: "#/components/schemas/Port" + destinationTrafficFilters: + description: Identifies the destination IP packet filters. To be + used when it is needed a traffic flow towards a specific Edge Application Server + interface identified by a protocol and a port. Also the Protocol + (e.g. TCP or UDP) can be specified. + type: object + properties: + destinationPort: + allOf: + - $ref: "#/components/schemas/Port" + destinationProtocol: + allOf: + - $ref: "#/components/schemas/Protocol" + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + required: + - apiConsumerId + - appId + PostTrafficInfluence: + description: inherits from TrafficInfluence restricting the access + (readonly) to "trafficInfluenceID" and "state", to be used by the API + Consumer to create a TrafficInfluece resource for any user. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + trafficInfluenceID: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + PostTrafficInfluenceDevice: + description: inherits from TrafficInfluence restricting the access + (read-only) to "trafficInfluenceID" and "state", to be used by the API + Consumer to create a TrafficInfluece resource for a specific user. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + device: + $ref: '#/components/schemas/Device' + trafficInfluenceID: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + PatchTrafficInfluence: + description: inherits from TrafficInfluence and restricts the access to + certain parameters. + Only some parameter can be indeed modified with the PATCH operation. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + trafficInfluenceID: + readOnly: true + apiConsumerId: + readOnly: true + appId: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.traffic-influence.v1.traffic-influence-change: "#/components/schemas/TrafficInfluenceNotification" + TrafficInfluenceNotification: + type: object + description: Notification channel for changes in the TrafficInfluence + resource. It returns back the TrafficInfluence resource with the + updated status ("state"). It provides back the identifiers + of the selected Edge Application Server instances. If more than one Device identifier was + provided, just the one used by the Traffic Influence API is returned. + allOf: + - $ref: "#/components/schemas/PostTrafficInfluenceDevice" + properties: + selected_appInstanceId: + type: array + items: + $ref: '#/components/schemas/AppInstanceId' + deviceResponse: + $ref: "#/components/schemas/DeviceResponse" + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required + in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/SubscriptionProtocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + SubscriptionProtocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.traffic-influence.v1.traffic-influence-change + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.traffic-influence.v1.traffic-influence-change + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ######################################################################## + # Types # + ######################################################################## + EdgeCloudZoneId: + type: string + format: uuid + description: | + Unique identifier created by the Edge Cloud Platform to identify an + Edge Cloud Zone within an Edge Cloud + EdgeCloudRegion: + type: string + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + additionalProperties: false + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device + identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the MNO might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible + across different MNOs. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In + mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to + E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile + network. In 3GPP terminology, it corresponds to the GPSI formatted with + the External Identifier ({Local Identifier}@{Domain Identifier}). + Unlike the telephone number, the network access identifier is not + subjected to portability ruling in force, and is individually managed + by each operator. + type: string + example: "123456789@domain.com" + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is not + in use) then the same address should be specified for both + publicAddress and privateAddress. + If NAT64 is in use, the device should be identified by its publicAddress + and publicPort, or separately by its allocated IPv6 address (field + ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + Protocol: + description: The protocol for the influenced flow. It can be specified and + it is identified by a string according to the column “Keyword” as defined + by IANA (https://www.iana.org/assignments/protocol-numbers/\ + protocol-numbers.xhtml), e.g. UDP or TCP. + type: string + example: "TCP" + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their + request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do not + match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers with a + given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + AppInstanceId: + type: string + format: uuid + description: A globally unique identifier associated with a running + instance of an application. OP generates this identifier. + AppId: + type: string + format: uuid + example: "6B29FC40-CA47-1067-B31D-00DD010662DA" + description: A globally unique identifier associated with the application. + OP generates this identifier when the application is submitted over NBI. + ######################################################################## + # Responses # + ######################################################################## + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The Traffic Influence resource identifier is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + - DENIED_WAIT + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + GENERIC_409_DENIED_WAIT: + description: Patch denial if the previous intent is not yet + fulfilled + value: + status: 409 + code: DENIED_WAIT + message: It is not possible to modify the Traffic Influence + resource because it is still under provisioning. The resource + can be modified when it is fully implemented and activated. + Please wait for the resource status (state) to be "active" + before trying to update it. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the + request and the device or phone number identification + cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when + a device or phone number has already been identified + from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the + access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. +``` diff --git a/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist/raw.md b/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9749f7a7c6b1f63bb8a44e4fc83518fa6663b56b --- /dev/null +++ b/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist/raw.md @@ -0,0 +1,33 @@ +# API Readiness Checklist + +Checklist for traffic-influence v0.10.0 in r.1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/traffic-influence.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.10.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/traffic-influence-user-story-use-case-1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [Device](/code/Test_definitions/traffic-influence-postTrafficInfluenceDevice.feature), [Every User](/code/Test_definitions/traffic-influence-postTrafficInfluence.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/d4JlBQ) | + + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + diff --git a/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1/raw.md b/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..9217a989f4b66b251061210782e8975be7deb239 --- /dev/null +++ b/marked/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1/raw.md @@ -0,0 +1,16 @@ +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service is provided by a Cloud instances of an Application. In a specific geographical area, the Service must be provided by an edge instance of the Application (EAS) for Premium users. The Application Function (AF) of the Service invokes the Traffic Influence API (exposed by the OP) to activate the appropriate routing at the Edge of the mobile network toward the local EAS Instance for the Premium Users. Premium Users access the service in that geographical area with the best user experience while Free users get a best effort service provided by the Cloud instances of the Service.| M | +|Roles, Actor(s) and scope|Application Function: role of Traffic Influence API consumer
                                        Operator Platform: role of Traffic Influence API provider
                                        User Equipment: role of Service consumer
                                        Edge Application Server: role of Service producer

                                        Scope: B2B use case to activate a specific traffic flow at the Edge toward an existing EAS in the Edge datacenters| M | +|NF Requirements|| O | +|Pre-conditions|• The EAS is deployed in the Edge datacenter
                                        • A connectivity between the Telco Edges (where the UPF is located) and the Edge datacenter (where the EAS Instance is located) is in place.| M | +|Begins when|The AF invokes the Traffic Influence API to have the fastest routing toward a specific EAS Instance.| M | +|Step 1|The OP authorizes the request (terminates with a notification to the AF if it is not valid)| M | +|Step 2|The Traffic Influence API Producer validates the request (terminates with a notification to the AF if it is not coherent with the policies)| M| +|Step 3|The API Producer checks for network resources to implement the request (terminates with a notification to the AF if not available)| M | +|Step 4|The API Producer configures the network resources to get the fastest routing toward the requested EAS Instance| M | +|Step 5|The API Producer notifies the AF that the requested routing has been activated. The API Producer returns and Identifier for the created resource| M | +|Step 6|The AF invokes the TI API as many times according to the number of users to be added to the resource (passing the resource identifier) (the cycle goes through Steps 2-3-4-5 each time)| M | +|Ends when|All the users are properly configured| M | +|Post-conditions|The traffic flow is routed from the selected UPF to the requested EAS Instance for the selected users| M | +|Exceptions|Step 4 can generate an exception to be notified to the AF| M | \ No newline at end of file diff --git a/marked/TrafficInfluence/documentation/SupportingDocuments/README/raw.md b/marked/TrafficInfluence/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/TrafficInfluence/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/VerifiedCaller/README/raw.md b/marked/VerifiedCaller/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..17e7de47058cf742287f27882cc9bf1b36caa567 --- /dev/null +++ b/marked/VerifiedCaller/README/raw.md @@ -0,0 +1,57 @@ + + + + + + + + + +# VerifiedCaller + +Sandbox API Repository to describe, develop, document, and test the VerifiedCaller Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/Pive) + +## Scope + +* Service APIs to deliver secure and branded calls (see “VerifiedCaller” within [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + * Announce a branded call via the Verified Caller API + * Register the content via Service Registration + * NOTE: The scope of these APIs should be limited (at least at the first stage) to calls made over 4G or 5G. +* Describe, develop, document, and test the APIs +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/VerifiedCaller/releases/tag/r1.3) (Fall25), with the following API versions: + * **brand-registration v0.1.0** + [[YAML]](https://github.com/camaraproject/VerifiedCaller/blob/r1.3/code/API_definitions/brand-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/brand-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/brand-registration.yaml) + * **verified-caller v0.1.0** + [[YAML]](https://github.com/camaraproject/VerifiedCaller/blob/r1.3/code/API_definitions/verified-caller.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/verified-caller.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/verified-caller.yaml) +* The latest public release is always available here: https://github.com/camaraproject/VerifiedCaller/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/VerifiedCaller/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/VerifiedCaller/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95553339882?password=c2022918-91d5-4d3d-9c4f-14b759b16e69) + * Schedule: bi-weekly (odd weeks), Thursday, 10:00 AM UTC (11:00 AM CET) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/1k9fcyv1) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/VerifiedCaller/code/API_definitions/brand-registration/raw.md b/marked/VerifiedCaller/code/API_definitions/brand-registration/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..3f41fc874665882238fc0718fa0db59c1869355a --- /dev/null +++ b/marked/VerifiedCaller/code/API_definitions/brand-registration/raw.md @@ -0,0 +1,900 @@ +# brand-registration + +```yaml +openapi: 3.0.3 +info: + title: Brand Registration + description: | + This API provides the ability to associate a calling party number with a human-readable string that is displayed to the callee on their device screen instead of the calling number. + + # Introduction + + Consumers of this API can associate calling party numbers with a human-readable string that is to be displayed to the callee on their device screen instead of the calling number. This allows the callee to recognize the caller even if the calling party number is not registered in the callee's device and increases the likelihood of the call being answered. + + Brand Registration API could be useful in scenarios such as: + - Telesales + - Customer Support + - Outreach efforts of NGOs. + - Calls placed by authorities or government institutions for official matters. + + # Relevant terms and definitions + * **phoneNumber** and **phoneNumberAlternate**: A pair of E.164 numbers representing the caller. Depending on the caller's networks access setup , only phoneNumber or both phoneNumber & phoneNumberAlternate may be used to uniquely identify the caller. The values typically correspond to parameters used in telecom signalling protocols, e.g. PAI and FROM headers in SIP. + * **displayName**: A human-readable string that is to be displayed to the callee on their device screen instead of the calling number. + * **displayAsset**: A visual asset (e.g. a logo, image or video) that is to be displayed to the callee on their device screen instead of the calling number. Support of the visual asset depends on the service provider and callee's device. If the service provider does not support the parameter, it SHALL clearly document the limitation and SHOULD silently ignore the parameter if received. + * **customerId** : A string to represent the owner of the displayName, e.g. a commercial brand or an institution. + * **verifyCallerAction**: An instruction applied during actual call setup. Indicates the action to be taken by the service provider if the authenticity of the caller cannot be established using VerifiedCaller API capabilities. + # API Functionality + + The API exposes the following endpoints/operations: + + - `/registrations` : + - **POST** operation creates a new registration and returns a registration identifier + - **GET** operation reads existing registrations from the brand registration service + - `/registrations/{registrationId}` : + - **PUT** operation updates an existing registration identified by the registrationId in the brand registration service + - **GET** operation reads an existing registration identified by the registrationId from the brand registration service + - **DEL** operation deletes an existing registration identified by the registrationId from the brand registration service + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/VerifiedCaller +servers: + - url: '{apiRoot}/brand-registration/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Create Brand registration + description: Create Brand Registration Information for a Calling Party + - name: Update Brand registration + description: Update Existing Brand Registration Information for a Calling Party + - name: Read Brand registration + description: Read Existing Brand Registration Information for a Calling Party + - name: Delete Brand registration + description: Delete Existing Brand Registration Information for a Calling Party +paths: + /registrations: + post: + tags: + - Create Brand registration + summary: Register new brand information in the service platform + description: Register new brand information with optional call verification request. + operationId: createRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateOrUpdateRegistrationRequest' + examples: + INPUT_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Create a registration for a device, identified by a phone number + value: + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + INPUT_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: Create a registration for a device, identified by a phone number & phone number alternate + value: + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + + responses: + '201': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Create404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/CreateOrUpdateRegistrationUnprocessableEntity422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:create + get: + tags: + - Read Brand registration + summary: Read existing brand registrations from the service platform + description: Read existing brand registrations from the service platform. + operationId: readRegistrations + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/Page' + - $ref: '#/components/parameters/PerPage' + - $ref: '#/components/parameters/Seek' + responses: + '200': + $ref: '#/components/responses/SuccessfulRecords' + '204': + $ref: '#/components/responses/204NoContent' + '206': + $ref: '#/components/responses/SuccessfulPartialRecords' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:read + + /registrations/{registrationId}: + get: + tags: + - Read Brand registration + summary: Read an existing brand registration from the service platform + description: Read an existing brand registration from the service platform + operationId: readRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + responses: + '200': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:read + delete: + tags: + - Delete Brand registration + summary: Delete an existing brand registration from the service platform + description: Delete an existing brand registration from the service platform + operationId: deleteRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + responses: + '204': + $ref: '#/components/responses/204NoContent' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:delete + put: + tags: + - Update Brand registration + summary: Update an existing brand registration in the service platform + description: Update an existing brand registration + operationId: updateRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateOrUpdateRegistrationRequest' + examples: + INPUT_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Update registration for a device, identified by a phone number + value: + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + INPUT_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: Update registration for a device, identified by a phone number & phone number alternate + value: + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + + responses: + '200': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Update404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/CreateOrUpdateRegistrationUnprocessableEntity422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:update + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: | + Indicates the subset of entries to be returned, where total number of pages is determined by the number of all applicable entries and the value of the *perPage* parameter. + *First page is indicated with value 0.* + schema: + type: integer + default: 0 + PerPage: + name: perPage + in: query + description: Indicates the number of entries to be returned in each response. Has no effect if total number of applicable entries < perPage. + schema: + type: integer + default: 10 + Seek: + name: seek + in: query + description: Indicates the last entry read, to create the next/previous subset of entries in the response of the current query. + schema: + type: string + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last entry provided in the response + schema: + type: string + X-Total-Count: + description: Total number of applicable entries + schema: + type: integer + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + RegistrationId: + type: string + format: uuid + description: Unique identifier of a registration created in the Branded Calling Platform as a result of the POST operation. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + CustomerId: + type: string + description: Unique customer identifier for a brand + example: "Customer1" + + DisplayName: + type: string + maxLength: 32 + description: Brand information that will be displayed for the calling party + example: "Company X Call Center" + + DisplayAsset: + type: string + format: uri + description: > + Resource URI for a visual asset (e.g. a logo, image or video) that is to be displayed to the called party. + The URI MAY be in IMS-style and include semicolon-separated URI parameters in accordance + with SIP / RFC 3261 conventions (e.g. ';purpose=icon'). + This URI is a logical identifier inside the service provider's network and is not guaranteed to be + resolvable by general-purpose HTTP clients. + Support of the DisplayAsset depends on the service provider and called party's device. + example: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + + VerifyCallerAction: + type: string + description: >- + Indicates if Antispoofing feature is enabled for the A-party, if enabled what action to take in case antispoofing check fails. Absence of parameter means feature not enabled. + example: "DO_NOT_BRAND" + enum: + - "BLOCK_UNVERIFIED" + - "DO_NOT_BRAND" + + TerminatingCountryCode: + type: integer + description: Country Code of the called number in E.164 format + example: 44 + + CampaignName: + type: string + description: Logical name to group a set of calling party numbers under a brand for a specific purpose, e.g. special charging + example: "Company X New Year Sales" + + CreateOrUpdateRegistrationRequest: + type: object + description: "Request object to create or update (replace) a brand registration" + required: + - "phoneNumber" + - "displayName" + - "terminatingCountryCode" + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + phoneNumberAlternate: + $ref: '#/components/schemas/PhoneNumber' + displayName: + $ref: '#/components/schemas/DisplayName' + displayAsset: + $ref: '#/components/schemas/DisplayAsset' + customerId: + $ref: '#/components/schemas/CustomerId' + verifyCallerAction: + $ref: '#/components/schemas/VerifyCallerAction' + terminatingCountryCode: + $ref: '#/components/schemas/TerminatingCountryCode' + campaignName: + $ref: '#/components/schemas/CampaignName' + + RegistrationRecord: + type: object + description: "Object to represent a single brand registration in the service platform" + required: + - "registrationId" + - "phoneNumber" + - "displayName" + - "terminatingCountryCode" + properties: + registrationId: + $ref: '#/components/schemas/RegistrationId' + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + phoneNumberAlternate: + $ref: '#/components/schemas/PhoneNumber' + displayName: + $ref: '#/components/schemas/DisplayName' + displayAsset: + $ref: '#/components/schemas/DisplayAsset' + customerId: + $ref: '#/components/schemas/CustomerId' + verifyCallerAction: + $ref: '#/components/schemas/VerifyCallerAction' + terminatingCountryCode: + $ref: '#/components/schemas/TerminatingCountryCode' + campaignName: + $ref: '#/components/schemas/CampaignName' + + RegistrationRecords: + type: array + items: + $ref: '#/components/schemas/RegistrationRecord' + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + SuccessfulRecord: + description: Success response with a brand registration record + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecord' + examples: + RECORD_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Registration for a device, identified by a phone number + value: + registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + RECORD_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: A registration for a device, identified by both a phone number and a phone number alternate + value: + registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + SuccessfulRecords: + description: Success response with one or more brand registration records + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecords' + examples: + TWO_RECORDS_FOUND: + summary: Two registration records available + description: Two registration records returned to the client + value: + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794833" + phoneNumber: "+123456790" + phoneNumberAlternate: "+123456791" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + customerId: "Customer2" + verifyCallerAction: "BLOCK_UNVERIFIED" + 204NoContent: + description: Successful response with no content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + SuccessfulPartialRecords: + description: | + Success response with one or more brand registration records. + Used if the request expects a paginated response. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecords' + examples: + TWO_RECORDS_FOUND: + summary: Two registration records available + description: Two registration records returned to the client + value: + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794833" + phoneNumber: "+123456790" + phoneNumberAlternate: "+123456791" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "BLOCK_UNVERIFIED" + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + summary: Unauthenticated + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Create404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + DEVICE_NOT_FOUND: + summary: Device not found + description: The device is not known to the service provider + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: 'The device is not known to the service provider' + Update404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + BRAND_REGISTRATION_404_REGISTRATION_NOT_FOUND: + summary: Registration not found + description: The brand registration service is not able to identify the registration + value: + status: 404 + code: BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + message: 'The brand registration service is not able to identify an existing registration' + DEVICE_NOT_FOUND: + summary: Device not found + description: The device is not known to the service provider + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: 'The device is not known to the service provider' + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + BRAND_REGISTRATION_404_REGISTRATION_NOT_FOUND: + summary: Registration not found + description: The brand registration service is not able to identify the registration + value: + status: 404 + code: BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + message: 'The brand registration service is not able to identify an existing registration' + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + summary: Conflict + description: Requested operation conflicts with existing data in the service platform + value: + status: 409 + code: CONFLICT + message: Requested operation conflicts with existing data in the service platform + CreateOrUpdateRegistrationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + summary: Generic Internal + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: "Internal server error" + Generic503: + description: Service unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + summary: Generic Unavailable + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" +``` diff --git a/marked/VerifiedCaller/code/API_definitions/verified-caller/raw.md b/marked/VerifiedCaller/code/API_definitions/verified-caller/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..748cc5054f19cc2dc262ee86f3b1a580c8ac81ff --- /dev/null +++ b/marked/VerifiedCaller/code/API_definitions/verified-caller/raw.md @@ -0,0 +1,500 @@ +# verified-caller + +```yaml +openapi: 3.0.3 +info: + title: Verified Caller + description: | + This API provides the ability to verify the authenticity of a call from a calling party to a specific called party. + + # Introduction + + Consumers of Verified Caller API can initiate the verification of the authenticity of a call from a calling party to a specific called party. A relationship between the API consumer and the service provider has to be already established for a calling party. This can be achieved by using the brand-registration API, or another mechanism agreed upon by the API consumer and the service provider. + + Verified Caller API could be useful in scenarios such as: + - Telesales + - Customer Support + - Outreach efforts of NGOs. + - Calls placed by authorities or government institutions for official matters. + + # Relevant terms and definitions + + * **callingParticipant** and **calledParticipant**: A pair of E.164 numbers representing the parties in a call. + * **registrationId** : A unique reference to the relationship between the API consumer and the service provider. + * **strategy**: Indicator of the requested method to be applied by the service provider to verify a call, as desired by the API consumer. + * **timeToLive**: The period for which the verification by the service provider remains valid. A call is not considered as verified if it is placed after expiry of verification. The service provider may choose to reject a request based on the requested timeToLive value, or apply a different value than requested by the API consumer. The service provider shall observe a timeToLive value for all accepted requests. In order to reduce the risk of a spoofed call, the service provider is advised to expire the verification right away once the call is placed. + * **dynamicDisplayName**: If strategy is 'BRAND_DISPLAY' and this parameter is provided, it overrides any pre-arranged display name presented to the callee, e.g. one set using the brand-registration API request. + + # API Functionality + The API exposes the following endpoints/operations: + - `/pre-announce` : + - **POST** operation creates a new pre-announcement for a call + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + Not applicable as this API requires the API consumer to identify the called party as the subject of the API using the mandatory `calledParticipant` object. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/VerifiedCaller +servers: + - url: '{apiRoot}/verified-caller/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Create Pre-announcement + description: Create a call pre-announcement for a Calling and a Called Party +paths: + /pre-announce: + post: + tags: + - Create Pre-announcement + summary: Create a call pre-announcement in the service platform + description: Create a call pre-announcement for a Calling and a Called Party that will remain valid for a specified duration. + operationId: createPreAnnouncement + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreatePreAnnouncementRequest' + examples: + USING_SMS: + summary: A short message is sent to the callee to verify authenticity of the caller + description: A short message is sent to the callee to verify authenticity of the caller + value: + callingParticipant: "+123456789" + calledParticipant: "+123456792" + strategy: "SMS" + timeToLive: 45 + registrationId: "d011cbff-cf79-4db3-a72b-8164aa894b37" + USING_BRAND_DISPLAY: + summary: A displayName is displayed to the callee to verify authenticity of the caller + description: A displayName is displayed to the callee to verify authenticity of the caller + value: + callingParticipant: "+123456791" + calledParticipant: "+123456792" + strategy: "BRAND_DISPLAY" + timeToLive: 45 + registrationId: "d011cbff-cf79-4db3-a72b-8164aa894b37" + dynamicDisplayName: "Company X Re: Your Complaint" + + responses: + '201': + $ref: '#/components/responses/Create201' + '204': + $ref: '#/components/responses/Create204' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Create404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/Create422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - verified-caller:create + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + PreAnnouncementId: + type: string + format: uuid + description: Unique identifier of a pre-announcement created as a result of the POST operation. Reserved for future use. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + TimeToLive: + type: integer + minimum: 1 + maximum: 86400 + description: This parameter specifies for how long the pre-announcement is valid, in units of seconds. Calls processed after the call pre-announcement expiry shall be treated as not announced. If not specified, the service provider applies a default value. The service provider may enforce an upper bound of their choosing while validating the request. + example: 60 + + RegistrationId: + type: string + format: uuid + description: Unique identifier of a relatonship created between the API consumer and the service platform. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + DynamicDisplayName: + type: string + maxLength: 32 + description: Brand information that will be displayed to the calling party if strategy is 'BRAND_DISPLAY'. If provided, this value overrides a pre-configured display name, e.g. the displayName parameter provided in the brand-registration API request. + example: "Company X Call Center" + + Strategy: + type: string + description: The method to be applied to verify the authenticity of the calling party. Absence of this parameter lets the service provider choose a default strategy which the API consumer must beware. + enum: + - "SMS" + - "BRAND_DISPLAY" + + CreatePreAnnouncementRequest: + type: object + description: "Request object to create a call pre-announcement" + required: + - "callingParticipant" + - "calledParticipant" + properties: + callingParticipant: + $ref: '#/components/schemas/PhoneNumber' + calledParticipant: + $ref: '#/components/schemas/PhoneNumber' + strategy: + $ref: '#/components/schemas/Strategy' + timeToLive: + $ref: '#/components/schemas/TimeToLive' + registrationId: + $ref: '#/components/schemas/RegistrationId' + dynamicDisplayName: + $ref: '#/components/schemas/DynamicDisplayName' + + ExpiresAt: + type: string + format: date-time + description: | + Date when the validity of call verification will expire. The call must be placed up to this date for the service provider to verfiy it. The service provider may inlcude it especially if the API consumer did not specify a timeToLive in the request, or the service provider chose to apply a different value than requested. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + + AnnouncementInfo: + type: object + description: "Object to represent the creation of a single pre-announcement in the service platform" + properties: + preAnnouncementId: + $ref: '#/components/schemas/PreAnnouncementId' + expiresAt: + $ref: '#/components/schemas/ExpiresAt' + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Create201: + description: Successful creation of a pre-announcement + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/AnnouncementInfo' + examples: + SUCCESSFUL_CREATION: + summary: Success response with optional parameters + description: Successful pre-announcement of a call. The service platform includes optional parameter(s) to inform the client. + value: + preAnnouncementId: "be5105dc-9b0e-437b-a03e-6e6ffb5e50c0" + expiresAt: "2023-07-03T12:27:08.312Z" + + Create204: + description: Successful creation of a pre-announcement with no content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + summary: Unauthenticated + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Create404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + DEVICE_NOT_FOUND: + summary: Device not found + description: Device is not found + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: "Call Participant {{number}} is not known to the service provider" + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + summary: Conflict + description: Requested operation conflicts with existing data in the service platform. That may point to a mismatch between the request and existing relationship between the API consumer and the service provider. + value: + status: 409 + code: CONFLICT + message: Requested operation conflicts with existing data in the service platform + Create422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + summary: Generic Internal + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: "Internal server error" + Generic503: + description: Service unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + summary: Generic Unavailable + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" +``` diff --git a/marked/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story/raw.md b/marked/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8fa005edcdb1f7809d031f0594bf28be1d2e6023 --- /dev/null +++ b/marked/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story/raw.md @@ -0,0 +1,24 @@ + +**User Story: Verified Caller - Registration** +
                                        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to register the display name to be announced for specified caller phone number in the Calling ID solution that I want to use. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                        **Actors:** Mobile Network Operators (MNO), Onboarding/Vetting authority, application developers, enterprise.
                                        **Scope:** | +| ***Pre-conditions*** |The preconditions are listed below:
                                        1. The Customer:User has provided mandatory information of their identity
                                        2. Application developer has onboarded to MNO API
                                        3. Application developer has API credentials
                                        | +| ***Activities/Steps*** | **Starts when:** The aggregator collect information (display names, phone numbers) and makes a request to the Verified Caller service (API) to register the caller information.
                                        **Ends when:** The MNO service returns an register id or an error.
                                        | +| ***Post-conditions*** | Branded information are verified and can be approved or rejected. The application developer can make decision to use this customer data to follow-up enterprise processes.| +| ***Exceptions*** | Several exceptions might occur during the Verified Caller API operations:
                                        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                        • Phone number already used by another customer
                                        • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                        | + +**User Story: Verified Caller - Pre-authorization (i.e. Pre-announcement)** +
                                        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to make my call verified and make the calling id solution displaying a branded announcement previously registered. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                        **Actors:** Mobile Network Operators (MNO), Onboarding/Vetting authority, application developers, enterprise.
                                        **Scope:** | +| ***Pre-conditions*** |The preconditions are listed below:
                                        1. The Customer:User has provided mandatory information of their identity
                                        2. Application developer has onboarded to MNO API
                                        3. Application developer has API credentials
                                        | +| ***Activities/Steps*** | **Starts when:** The enterprise wants its branded company name be displayed when calling a phone number to avoid any spoofing .
                                        **Ends when:** The MNO service returns an acknowledgment or an error.
                                        | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the Verified Caller API operations:
                                        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                        • Not Found: The called or caller phone number provided is not managed by the MNO
                                        • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                        | diff --git a/marked/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist/raw.md b/marked/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..71f450ad00f608583bc29e938f1911994fcd715a --- /dev/null +++ b/marked/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Brand Registration v0.1.0 in r1.3. + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [brand-registration.yaml](/code/API_definitions/brand-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [VerifiedCaller_User_Story.md](/documentation/API_documentation/VerifiedCaller_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/WwPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist/raw.md b/marked/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1d8fae300c375e2918ab785d06da8fdfc1ba1c12 --- /dev/null +++ b/marked/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist/raw.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Verified Caller v0.1.0 in r1.3. + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-----------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [verifiedcaller-preannounce.yaml](/code/API_definitions/verifiedcaller-preannounce.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [VerifiedCaller_User_Story.md](/documentation/API_documentation/VerifiedCaller_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/WwPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/marked/VoiceNotification/README/raw.md b/marked/VoiceNotification/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..31ff8d9736b307a81857b1a8695d72458d1f9ab8 --- /dev/null +++ b/marked/VoiceNotification/README/raw.md @@ -0,0 +1,43 @@ + + + + + + + + + +# VoiceNotification + +Sandbox API Repository to describe, develop, document, and test the VoiceNotification Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/owAbBw) + +## Scope + +* Service API(s) “VoiceNotification” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: May 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/owAbBw) !! update this link to your minutes archive page using the "Share" link and delete the task +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/VoiceNotification/code/API_definitions/README/raw.md b/marked/VoiceNotification/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/VoiceNotification/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/VoiceNotification/documentation/API_documentation/README/raw.md b/marked/VoiceNotification/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/VoiceNotification/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/VoiceNotification/documentation/SupportingDocuments/README/raw.md b/marked/VoiceNotification/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/VoiceNotification/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/VoiceVerificationCode/README/raw.md b/marked/VoiceVerificationCode/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1b50b319a49ae0326c0151945718c0cdd5f14599 --- /dev/null +++ b/marked/VoiceVerificationCode/README/raw.md @@ -0,0 +1,42 @@ + + + + + + + + + +# VoiceVerificationCode + +Sandbox API Repository to describe, develop, document, and test the VoiceVerificationCode Service API(s) within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/nID7Bw) + +## Scope + +* Service API(s) “VoiceVerificationCode” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! ⚠️ Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: June 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/nID7Bw) !! update this link to your minutes archive page using the "Share" link and delete the task +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/marked/VoiceVerificationCode/code/API_definitions/README/raw.md b/marked/VoiceVerificationCode/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/VoiceVerificationCode/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/VoiceVerificationCode/documentation/API_documentation/README/raw.md b/marked/VoiceVerificationCode/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/VoiceVerificationCode/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/VoiceVerificationCode/documentation/SupportingDocuments/README/raw.md b/marked/VoiceVerificationCode/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/VoiceVerificationCode/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/WebRTC/README/raw.md b/marked/WebRTC/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..941a7f1f37b2848e307d54bf31df5fecc54549de --- /dev/null +++ b/marked/WebRTC/README/raw.md @@ -0,0 +1,71 @@ + + + + + + + + + +# WebRTC + +Sandbox API Repository to describe, develop, document, and test the WebRTC Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/MS7e) + +## Scope +* Service APIs for “WebRTC” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Add real-time communication capabilities to their applications like video, voice, and generic data. + * Enable an API consumer to register for communication services through a network using Oauth 2.0 and OIDC. + * Create subscriptions to receive call notifications using CloudEvents: Ability to follow the call establishment process and to receive new incoming calls. + * Make and receive calls from the API consumer (client) side establishing a realiable media session to securely exchange media. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: September 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/WebRTC/releases/tag/r2.2) (Fall25), with the following API versions: + * **webrtc-call-handling v0.3.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-call-handling.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-call-handling.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-call-handling.yaml) + * **webrtc-events v0.2.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-events.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-events.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-events.yaml) + * **webrtc-registration v0.3.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-registration.yaml) +* The latest public release is always available here: https://github.com/camaraproject/WebRTC/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/WebRTC/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/WebRTC/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## API Extra documentation + +* Find API reference documentation at folder: [code/API_definitions](code/API_definitions/) +* Find API testing documentation at folder: [code/Test_definitions](code/Test_definitions/) +* Find release status documentation at folder: [documentation/API_documentation](documentation/API_documentation) +* Find UML and complementary documentation at folder: [documentation/SupportingDocuments](documentation/SupportingDocuments) +* For other information refer to [Confluence CAMARA project wiki](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14560817/WebRTC) + +## Meetings +* Meetings are held virtually + * Find meeting notes at https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564608/Minutes+-+WebRTC +* Schedule: + * Tuesdays 4pm CEST (Madrid, Paris, Berlin, Rome), each 15 days + +## Contributorship and mailing list + +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/marked/WebRTC/code/API_definitions/README/raw.md b/marked/WebRTC/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e1c2d5a4749f1ed657e32cfbb734d601920f4b62 --- /dev/null +++ b/marked/WebRTC/code/API_definitions/README/raw.md @@ -0,0 +1,47 @@ +# WebRTC APIs definitions + +This folder contain the OpenAPI definitions of the WebRTC subgroup + +## APIs included + +* `webrtc-registration` [Registration and Authentication management](webrtc-registration.yaml) + * This API definition provides functionality for a REST client, browser or native application to manage Registration and Connectivity (RACM) towards Internet Multimedia Subsystem (IMS) Network. + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-registration.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-registration.yaml) + +* `webrtc-call-handling` [Call handling service](webrtc-call-handling.yaml) + * This API definition provides functionality for REST clients, browser or native application, to create and manage 1-1 calling. Both incoming and outgoing. + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-call-handling.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-call-handling.yaml) + +* `webrtc-events` [WebRTC Event Subscription](webrtc-events.yaml) + * This API definition provides functionality for REST clients, browser or native application, to track session events. This will allow the client to receive server side updates about new incoming calls and other needed updates regarding the media negotiation and session progress (ringing, hangup, etc). + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-events.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-events.yaml) + +Detailed descriptions, diagrams and more information could be found at [API documentation](../../documentation/API_documentation/) section + +## Check APIs online + +Use the previous links to check the DEV main version of the API. Copy & paste any raw file to check them: + +* ReDoc: https://redocly.github.io/redoc/ +* Swagger: https://editor.swagger.io/ +* CAMARA dedicated swagger instance: https://camaraproject.github.io/swagger-ui/ + + +## Build HTML from sources + +Build an HTML from sources using a local build OpenAPI v3 compatible like Node `redocly/cli` + +Execute redocly for each API document, use -o to +``` +$ npx @redocly/cli build-docs API_description_file.yaml +``` + +Or install the tool globaly and then build it +``` +$ npm install @redocly/cli -g + +$ redocly build-docs API_description_file.yaml +``` \ No newline at end of file diff --git a/marked/WebRTC/code/API_definitions/webrtc-call-handling/raw.md b/marked/WebRTC/code/API_definitions/webrtc-call-handling/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..0ebb6ddcb7ff0c860ddd078d51bc7b2053863316 --- /dev/null +++ b/marked/WebRTC/code/API_definitions/webrtc-call-handling/raw.md @@ -0,0 +1,922 @@ +# webrtc-call-handling + +```yaml +openapi: 3.0.3 +info: + title: WebRTC Call Handling + description: |- + # Introduction + + This API provides REST API for clients to manage live audio and video sessions + towards the operator's network (IMS network). + + To handle audio/video sessions, what we usually known as *calls*, the network + requires to identify both involved parties: caller, the origin, and the callee, + the destination. Once the involved communication endpoints are identified, + the endpoints need to negotiate *how* to send media from one endpoint to the other. + + The first step, *identify the endpoints* is handled through + parameters in the API request. The latter step, *negotiate how to connect*, is done by + sharing media transmission requirements (called SDP information) between the involved endpoints. + + In this step, the WebRTC technology is used to simplify the access to the + media, and get a simple and well-known protocol to negotiate the media transmission + requirements. + + Let's dig into more details on section 3: API functionality + + **Use cases to cover:** + - Functional: + - Ability to create audio and video sessions on the network, this grants + ability to reach any phone number on the public network using your telco + provider rights. + - Ability to retrieve any session, to recover for a network disconnection + or to check current status for any reason. + - Ability to upgrade to video, change sending audio/video parameters, or + notify the network about any modification on your side of the calls. + - Ability to hangup the call. Stop the transmission, and delete your audio + and video session. + - An additional subscription to webrtc-events API is required to receive + incoming events from network side (ex. remote hangup event). + + # Relevant terms and definitions + + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a **media session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **deviceId**: A unique identifier for the physical device where a media + session is initiated. It is provided by the WebRTC application, it remains + consistent across multiple installations or logins on the same device. Its + primary function is to ensure that only one WebRTC session (**registration**) + is active per device at a time, enabling the network to clean up any stale + sessions if a new session is initiated on the same device. + - **registration**: A device status in which the device is properly + identified and recognized as reachable by the server side of the network. + - **registrationId**: Unique identifier of an device **registration**. + Retrieved using the `webrtc-registration` API + - **x-correlator**: Unique ID included in the API request created by the API consumer. + It is used to correlate an API request with its response and help in debugging. + - **WebRTC**: WebRTC is a free and open-source project providing web browsers + and mobile applications with real-time communication via application programming + interfaces. It allows audio and video communication and streaming to work + inside web pages by allowing direct peer-to-peer communication + - **SDP**: Acronym for Session Description Protocol. The SDP is a format for + describing multimedia communication sessions for the purposes of announcement + and invitation. + - **WrtcSDPDescriptor**: Schema to include inside a JSON, a SDP body. You can + obtain an SDP for WebRTC calling using the WebRTC API provided by the browser + or any other media library. + + # API functionality + + This API allows to create 1-1 voice and video sessions. These, identified by a + unique `mediaSessionId` can be recovered, updated and terminated via this API + and its methods. + - **POST**: Create a new session using a valid `registrationId` from registration API + - **GET**: Recover an existing session via its unique `mediaSessionId` + - **DELETE**: Finish an existing session via its unique `mediaSessionId` + - **PUT**: Update the status of a session via its unique `mediaSessionId` + + To receive updates from the network about the session establishment process, you + must use `webrtc-events` API. + + ## 1. Creating a call + + To call someone, you need, previously a valid registration on the network. + You must check the webrtc-registration API to retrieve a valid registration + on the network that allows you to send calls (IMS registration). + + Once this is completed, you can consume the POST /sessions/ endpoint to call + a remote destination. + + ``` + POST /webrtc-call-handling/v0.2/sessions + { + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + } + ``` + + This will create a call, but without local media you will have a problem, or + maybe the network will reject your call. You need to add a local SDP offer. + + > **The WebRTC SDP local candidate** + > + > What is usually done, before attempt to create a call, is to solve the SDP local + description. This is, how you are going to send the media. To explain it briefly, + browsers offer the + [WebRTC API](https://developer.mozilla.org/en-US/docs/Web/API/WebRTC_API) that + include `getUserMedia()` and `RTCPeerConnection` interfaces that will simplify + the process. + > + > In summary, we need to obtain the media, create the `RTCPeerConnection` + and use it's SDP on our CAMARA webrtc-call-handling API as the offer. There + is extra information about this concept on the SupportingDocuments folder. + + Once you retrieve you local SDP offer, you modify your session including it, + or maybe you prefer to solve the local candidate before attempt the call, in + that case, you will include your local offer on the audio/video session creation. + + ``` + POST /webrtc-call-handling/v0.2/sessions + { + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + "offer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + } + } + ``` + + Following this point, your call is progressing and the network will inform + about extra information required and connection status via de the + webrtc-events API. + + Check webrtc-events API inline documentation and supporting documents + for further information. + + ## 2. Hanging up a call + + When you have a voice/video session in progress, you can decide to finish the + call, to do so, simply execute a DELETE request of the session using the + `mediaSessionId` obtained on call creation. + + This action will trigger all necessary action on the network side to properly + hangup and drop the call. + + ## 3. Picking up a call + + Using the `webrtc-events` API, you can receive events from the network, these + events could include the `session-invitation` event. This means that someone + is calling you. + + To *hook off*, we need to retrieve the session based on the `mediaSessionId` + using the GET request, afterwards, you can present to the user some + confirmation option to accept the call. + + Final step is to include a local offer. We already seen at 3.1 that a local + SDP is required, in this case, we will use the PUT request to modify the + audio/video session and include the information about the responding device. + + Let's say that we are responding this session `0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD`: + ``` + PUT /webrtc-call-handling/v0.2/sessions/0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD/status + { + "status": "InProgress", + "answer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + } + } + ``` + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Emergency Calling + - Introduces a new `callType` attribute with values `REGULAR` or `EMERGENCY`. + - When `callType` is `EMERGENCY`, the client **MAY** include `locationDetails` + describing the caller's location. + - `locationDetails` follows PIDF-LO concepts (3GPP TS 24.229, RFC 4119, RFC 5139, + RFC 5491) with either a circle or ellipsoid shape. + - If `callType` is omitted, it defaults to `REGULAR`. + + license: + name: Apache 2.0 + url: 'https://www.apache.org/licenses/LICENSE-2.0.html' + version: 0.3.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: '{apiRoot}/webrtc-call-handling/v0.3' + variables: + apiRoot: + description: API root + default: 'http://localhost:9091' +tags: + - name: Call handling + description: Operations to manage voice video sessions (calls) +paths: + /sessions: + post: + tags: + - Call handling + summary: Creates voice and/or video session + description: Creates a voice and/or video session + operationId: createSession + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/hdrRegistrationId' + security: + - openId: + - webrtc-call-handling:sessions:create + requestBody: + description: Provide the information required for session creation + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Media session request: + $ref: '#/components/examples/exampleMediaSessionRequest' + EmergencyMediaSessionRequest: + $ref: '#/components/examples/exampleEmergencyMediaSessionRequest' + responses: + '201': + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + SessionCreated: + $ref: '#/components/examples/exampleMediaSessionResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: '#/components/responses/Generic403' + '501': + description: Not Implemented + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - CALLTYPE_EMERGENCY_NOT_SUPPORTED + examples: + 501_CALLTYPE_EMERGENCY_NOT_SUPPORTED: + description: The implementation of API provider does not support the `callType` of `EMERGENCY`. + value: + status: 501 + code: CALLTYPE_EMERGENCY_NOT_SUPPORTED + message: Server does not support call type EMERGENCY. + /sessions/{mediaSessionId}: + get: + tags: + - Call handling + summary: Get the media session information + description: | + Get the media Session description based on `mediaSessionId`. + + ** The client shall construct the API path using the `mediaSessionId` supplied + in the session creation response (origination) or in the invitation notification + (termination). ** + operationId: getSessionDetailsById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:read + responses: + '200': + description: A session information + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + delete: + tags: + - Call handling + summary: Cancel or Terminate the media session + description: > + Cancel a 1-1 media session (as originator), + + Decline a 1-1 media session (as receiver), + + Terminate a 1-1 an ongoing media session + + ** The client shall construct the API path using the mediaSessionId supplied in the session creation response (origination) or in the invitation notification (termination). **' + operationId: deleteSessionById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:delete + responses: + '204': + description: Session deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + /sessions/{mediaSessionId}/status: + put: + tags: + - Call handling + summary: Update the status of the media session + description: | + Update the status of the media session, this may include updating SDP media + + The API consumer shall construct the API path using the `mediaSessionId` supplied in the session creation response (origination) or in the invitation notification (termination). + operationId: updateSessionStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:write + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Update inProgress (update media candidates): + $ref: '#/components/examples/exampleSessionStatus183InProgress' + Update ringing (device user endpoint is ringing): + $ref: '#/components/examples/exampleSessionStatus180Ringing' + Update connected (call is established): + $ref: '#/components/examples/exampleSessionStatus200Connected' + Update hold (call has been placed on call waiting mode): + $ref: '#/components/examples/exampleSessionStatusHold' + Update resume (call has been resumed): + $ref: '#/components/examples/exampleSessionStatusResume' + responses: + '200': + description: | + Updated the session status (with SDP data). + It will confirm the status defined on the PUT operation. + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Update inProgress (update media candidates): + $ref: '#/components/examples/exampleSessionStatus183InProgress' + Update ringing (device user endpoint is ringing): + $ref: '#/components/examples/exampleSessionStatus180Ringing' + Update connected (call is established): + $ref: '#/components/examples/exampleSessionStatus200Connected' + Update hold (call has been placed on call waiting mode): + $ref: '#/components/examples/exampleSessionStatusHold' + Update resume (call has been resumed): + $ref: '#/components/examples/exampleSessionStatusResume' + '204': + description: Updated the session status (no content) + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + hdrRegistrationId: + name: registrationId + in: header + description: The device registration identifier assigned by the network + required: true + style: simple + explode: false + schema: + type: string + pathParamMediaSessionId: + name: mediaSessionId + in: path + description: The sessionId assigned by the network for the media session + required: true + style: simple + explode: false + schema: + type: string + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + MediaSessionInformation: + type: object + properties: + originatorAddress: + $ref: '#/components/schemas/Address' + originatorName: + type: string + description: Friendly name of the call originator + example: 'Alice' + receiverAddress: + $ref: '#/components/schemas/Address' + receiverName: + type: string + description: Friendly name of the call terminator + example: 'Bob' + status: + $ref: '#/components/schemas/SessionStatus' + offer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + answer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + mediaSessionId: + type: string + description: >- + The media session ID created by the network. The mediaSessionId shall not be + included in POST requests by the client, but must be included in the notifications + from the network to the client device. + example: 0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF + callType: + type: string + description: Type of call. When set to EMERGENCY, the client MAY provide locationDetails. If omitted, treated as REGULAR. + enum: + - REGULAR + - EMERGENCY + locationDetails: + $ref: '#/components/schemas/LocationDetails' + WrtcSDPDescriptor: + type: object + description: |- + **OFFER**: An inlined session description in SDP format [RFC4566].If XML syntax + is used, the content of this element SHALL be embedded in a CDATA + section. + + **ANSWER**: This type represents an answer in WebRTC Signaling. This element is not + present in case there is no answer yet, or the session invitation has + been declined by the Terminating Participant.This element MUST NOT be + present in a request from the application to the server to create a + session. + properties: + sdp: + type: string + description: |- + An inlined session description in SDP format [RFC4566].If XML syntax is used, the content of this element SHALL be embedded in a CDATA section + SessionStatus: + type: string + description: Provides the status of the media session. During the session creation, this attribute SHALL NOT be included in the request. + enum: + - Initial + - InProgress + - Ringing + - Proceeding + - Connected + - Terminated + - Hold + - Resume + - SessionCancelled + - Declined + - Failed + - Waiting + - NoAnswer + - NotReachable + - Busy + example: Ringing + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represent + Address: + type: string + description: Subscriber address (Sender or Receiver) + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,}|urn:service:sos(?:\.[a-z0-9](?:[a-z0-9\-]{0,30}[a-z0-9])?)*)$' + example: 'tel:+11234567899' + LocationDetails: + type: object + description: Details about the caller's location and related information. This + object adheres to 3GPP TS 24.229, RFC 4119, RFC 5139, and RFC 5491 for PIDF-LO + compatibility. + properties: + shape: + type: string + enum: + - Circle + - Ellipsoid + description: The shape representing the caller's location (Circle or Ellipsoid). + coordinates: + oneOf: + - $ref: '#/components/schemas/CircleCoordinates' + - $ref: '#/components/schemas/EllipsoidCoordinates' + description: The coordinates of the caller's location, specific to the chosen + shape. + method: + type: string + enum: + - GPS + - DBH + - DBH_HELO + - Other + description: 'The method used to obtain the location information. + + * **GPS:** Global Positioning System (highly accurate) + + * **DBH:** Device-Based Hybrid + + * **DBH_HELO:** Device-Based Hybrid using Apple Hybridized Emergency Location + + * **Other:** Other methods (e.g., landmarks, IP Based etc.) + + ' + confidence: + type: object + description: The confidence level of the location information. + properties: + pdf: + type: string + enum: + - normal + - uniform + description: The probability density function (PDF) associated with the + confidence value. + value: + type: number + minimum: 0 + maximum: 100 + description: The confidence value (percentage). + timestamp: + type: string + format: date-time + description: The timestamp (in ISO 8601 format) indicating when the location + information was Calculated. \nThis is crucial for emergency services to + assess the timeliness of the data. if not provided current timestamp will + be used by default" + CircleCoordinates: + type: object + required: + - latitude + - longitude + - radius + properties: + latitude: + type: number + format: float + description: Latitude of the center point in decimal degrees (WGS84). + longitude: + type: number + format: float + description: Longitude of the center point in decimal degrees (WGS84). + radius: + type: number + format: float + description: Radius of the circle in meters, indicating the uncertainty. + EllipsoidCoordinates: + type: object + required: + - latitude + - longitude + - zAxis + - semiMajorAxis + - semiMinorAxis + - verticalAxis + - orientation + properties: + latitude: + type: number + format: float + description: Latitude in the WGS 84 geocentric coordinate system. + longitude: + type: number + format: float + description: Longitude in the WGS 84 geocentric coordinate system. + zAxis: + type: number + format: float + description: Altitude (optional) in the WGS 84 geocentric coordinate system. + semiMajorAxis: + type: number + description: Length of the semi-major axis of the ellipsoid in meters. + semiMinorAxis: + type: number + description: Length of the semi-minor axis of the ellipsoid in meters. + verticalAxis: + type: number + description: Length of the vertical axis of the ellipsoid in meters. + orientation: + type: number + description: Orientation of the ellipsoid in degrees. + examples: + exampleMediaSessionRequest: + value: + originatorAddress: tel:+17085852753 + originatorName: tel:+17085852753 + receiverAddress: tel:+17085854000 + receiverName: tel:+17085854000 + offer: + sdp: "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:2448:7a05:9b11:66f2:c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:Xm3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\n" + exampleMediaSessionResponse: + value: + originatorAddress: 'tel:+17085852753' + originatorName: 'tel:+17085852753' + receiverAddress: 'tel:+17085854000' + receiverName: 'tel:+17085854000' + offer: + sdp: "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:2448:7a05:9b11:66f2:c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:Xm3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\n" + status: Initial + mediaSessionId: 0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD3F90AE0CEB9EEB0C0F703E199FC00E7C6E648F50EE885FF0CE6C7E1CEE795EDD + exampleSessionStatus183InProgress: + value: + receiverSessionStatus: + status: InProgress + answer: + sdp: > + "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 + 0\r\nm= + + audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 + 2001:e0:410:2448:7a05:9b11:66f2 + + :c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 + 0.0.0.0\r\na=candidate:1645903805 1 udp + + 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typhost + generation 0 + + network-id 3 network-cost + 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9 + + ggaqxBlHbAFMx\r\na=ice-options:trickle + renomination\r\na=mid:audio\r\na= + + extmap:2 + http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions + + -01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 + AES_CM_128_HMAC_SHA1_80 inline:Xm + + 3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 + AMR-WB/16000\r\na=fmtp:102 + + octet-align=0; mode-set=0,1,2; + mode-change-capability=2\r\na=rtpmap:113 + telephone-event/16000\r\n" + exampleSessionStatus180Ringing: + value: + receiverSessionStatus: + status: Ringing + exampleSessionStatus200Connected: + value: + receiverSessionStatus: + status: Connected + answer: + sdp: > + "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 + 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN + + IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN + IP4 0.0.0.0\r\na=candidate:3108871805 1 udp + + 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host + generation 0 network-id 3 network-cost 900\r\na= + + ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle + renomination\r\na=mid:audio\r\na= + + extmap:2 + http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r + + \na=crypto:1 AES_CM_128_HMAC_SHA1_80 + inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 + AMR-WAB/16000 + + \r\na=fmtp:102 octet-align=0; mode-set=0,1,2; + mode-change-capability=2\r\na=rtpmap:113 + telephone-event/16000\r\na= + + ptime:20\r\n" + exampleSessionStatusHold: + value: + ReceiverSessionStatus: + status: Hold + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + exampleSessionStatusResume: + value: + ReceiverSessionStatus: + status: Resume + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + exampleEmergencyMediaSessionRequest: + summary: Emergency call initiation with location details + value: + originatorAddress: 'tel:+17085852753' + originatorName: Alice + receiverAddress: 'urn:service:sos' + receiverName: PSAP + offer: + type: offer + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + callType: EMERGENCY + locationDetails: + shape: Circle + coordinates: + latitude: 47.6062 + longitude: -122.3321 + radius: 35 + method: GPS + confidence: + pdf: normal + value: 92 + timestamp: '2025-10-06T19:31:25Z' + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "originator info is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. +``` diff --git a/marked/WebRTC/code/API_definitions/webrtc-events/raw.md b/marked/WebRTC/code/API_definitions/webrtc-events/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..78a4d5668279618c46e611598466988183800f72 --- /dev/null +++ b/marked/WebRTC/code/API_definitions/webrtc-events/raw.md @@ -0,0 +1,1595 @@ +# webrtc-events + +```yaml +openapi: 3.0.3 +info: + title: WebRTC Events + description: |- + # Introduction + + This API provide REST API for a client, browser or native application, to + receive events about updates of an active session or new sessions requests + (incoming calls) or registration termination. + + This API allows a WebRTC client to subscribe to events associated with a specific device, + identified by its `deviceId`. The deviceId uniquely represents a physical device on which + registrations and sessions may occur. + + Instead of requiring separate subscriptions per registration (`registrationId`) or per session + (`mediaSessionId`), event delivery is consolidated under the deviceId. This enables the client to + receive all relevant notifications — such as new call invitations or session status updates — + for any registration or session belonging to the same device. + + This allows the device applications to update the UI while media sessions + are progressing and also, allows the device to receive new session request, + generating incoming call scenarios for non-SIM devices. + + A classic use case is the negotiation of a live media session (call), that + requires multiple asynchronous events from server side. Other classic + example, is to notify that a subscriber is not logged into the network + anymore and requires refresh, for example, when the IMS expires the + device registration. + + In addition, this API, allows to an external service to create "notification + channels" for other systems that does no support the async event mechanisms. + For instance, a classic browser using websockets to receive server-side + events. + + **Use cases to cover:** + - Functional: + - A push notification service based on an external webhook + - A browser that requires a WS to receive events from the server side. + - This will require to create a dedicated endpoint using another + network API or external system. + - Observability: + - A monitoring system that wants to monitor registration status of + devices + - A call audit application that requires to remotely monitor call status + + # Relevant terms and definitions + + - **BYON**: Bring Your Own Number. A commercial name for the functionality + to use your network credentials and phone number identity to non-SIM + devices using media sessions. + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a Voice or Video **session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **registration**: A device status in which the device is properly + identified and recognized as reachable by the server side of the network. + - **registrationId**: Unique identifier of an device **registration**. + Retrieved using the `webrtc-registration` API + + # API functionality + + The CAMARA subscription model is detailed in the CAMARA API design guideline + document and follows CloudEvents specification. + + This API allows to create an explicit notification channel for two types of + events. It is mandatory in the subscription to provide the event type for + which the client would like to subscribe. + + Following event types are managed for this API: + + - `org.camaraproject.webrtc-events.v0.session-status` + + - Events triggered for any media session related event (e.g. far end new + media endpoints) + + - `org.camaraproject.webrtc-events.v0.session-invitation` + + - Events triggered when a new session is requested (e.g. incoming call + received) + + - `org.camaraproject.webrtc-events.v0.registration-ends` + + - Events triggered when a webrtc registration is terminated (e.g. webrtc registration expired) + + Note: Additionally to these list, ``org.camaraproject.webrtc-events.v0.subscription-ended`` + notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used when: + - the subscription expire time has been reached (optionally set by the + requester) + - the maximum number of subscription events has been reached (optionally + set by the requester) + - the subscription was deleted by the requester + - the Access Token `sinkCredential` expiration time has been reached + (optionally set by the requester) + - the API server has to stop sending notification prematurely + + ## 1. Session events (session-status) + + Find more information at the Schema description. + + A `org.camaraproject.webrtc-events.v0.session-status` event includes + session information updates. With the same schema that is used with the + WebRTC Call Handling API, when retrieving information from the + `GET /webrtc-call-handling/session/{mediaSessionId}` endpoint. + + In general lines, it is emitted each time that an event happens within the + subscribed session. This might happen when SDP updates are included for any + party or when the call is finished due an ordered cleanup or a service + outage. Any other any relevant internal event could be transmitted through + this channel (eg.: Any SIP response is potentially a + session-status event. + + Regarding the SDP descriptions for offer and answer: + - The offer, which MUST be present in a request from the application to the + server to create a session. Note that the offer can be absent in a session + created by the server as part of an offerless INVITE [RFC3261]. + - For the answer. This type represents an answer in WebRTC Signaling. This + element is not present in case there is no answer yet, or the session + invitation has been declined by the Terminating Participant. This element + MUST NOT be present in a request from the application to the server to + create a session. + + ## 2. New session request (session-invitation) + + Find more information at the Schema description. + + A `org.camaraproject.webrtc-events.v0.session-invitation` event + includes information about new requested sessions (incoming calls), it + requires a valid registration on the network. + + This event is triggered each time that the endpoint is requested to join + an incoming new session. This is done, usually, to indicate that a new + media "call" is incoming. In practical terms, this is a new media + session that requests the endpoint presence. The event include all + functional information required to join the session (media info, caller). + + When a new session is requested, it will include context information: + identification of the caller and other possible carrier data to + contextualize (call subject, branding info, etc). It will also include + a unique SessionId, to create a dedicated subscription and receive events + about the session itself and its status progressing inside the network. + + ## 3. Subscription ends (subscription-ended) + + A `org.camaraproject.webrtc-events.v0.subscription-ended` event indicates that + the endpoint will no longer be notified when a new event occurs. From + the developer's point of view, receiving the subscription-ended event should + signal the need to check the event subscription status and attempt to refresh + it in order to continue receiving new event notifications. + + ## 4. Registration ends (`registration-ends`) + + A `org.camaraproject.webrtc-events.v0.registration-ends` event indicates that a previously active registration has ended and is no longer valid. + From a developer's point of view, reception of the `registration-ends` event should be treated as a signal to renew the WebRTC registration in order to continue receiving or initiating calls for the registered phone number. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.2.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: "{apiRoot}/webrtc-events/v0.2" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Webrtc-events Subscription + description: |- + Operations to manage event subscriptions for WebRTC Event APIs. + Directly related with webrtc-call-handling and webrtc-registration. +paths: + /subscriptions: + post: + tags: + - Webrtc-events Subscription + summary: "Create a webrtc-events event subscription" + description: |- + Create a webrtc-events event subscription. For the corresponding type: + + - `org.camaraproject.webrtc-events.v0.session-invitation`: new calls event + - `org.camaraproject.webrtc-events.v0.session-status`: updates on specific call + - `org.camaraproject.webrtc-events.v0.registration-ends`: registration termination event + + To subscribe and receive notifications about new calls, a + `session-invitation` subscription is required using the `deviceId` related to a valid registration. + + operationId: createNotificationChannelSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - webrtc-events:org.camaraproject.webrtc-events.v0.session-status:create + - webrtc-events:org.camaraproject.webrtc-events.v0.session-invitation:create + - webrtc-events:org.camaraproject.webrtc-events.v0.registration-ends:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + INVITE_SUBSCRIPTION (session-invitation): + $ref: "#/components/examples/INVITE_SUBSCRIPTION" + SESSION_SUBSCRIPTION (session-status): + $ref: "#/components/examples/SESSION_SUBSCRIPTION" + REGISTRATION_ENDS_SUBSCRIPTION (registration-ends): + $ref: "#/components/examples/REGISTRATION_ENDS_SUBSCRIPTION" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: |- + Important: this endpoint is to be implemented by the API + consumer. The webrtc-events server will call this endpoint + whenever a webrtc-events event occurs. `operationId` value will + have to be replaced accordingly with WG API specific semantic. + operationId: createNotificationChannelSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + NEW_SESSION_INCOMING (session-invitation): + $ref: "#/components/examples/NEW_SESSION_INCOMING" + SESSION_UPDATE (session-status): + $ref: "#/components/examples/SESSION_UPDATE" + REGISTRATION_EXPIRED (registration-ends): + $ref: "#/components/examples/REGISTRATION_ENDS" + SUBSCRIPTION_ENDED (subscription-ended): + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Webrtc-events Subscription + summary: "Retrieve a list of webrtc-events event subscription" + description: + Retrieve **a list** of webrtc-events subscription(s) with detailed + information. Including configuration data and current status. + operationId: retrieveNotificationChannelSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - webrtc-events:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Webrtc-events Subscription + summary: "Retrieve a webrtc-events event subscription" + description: | + Retrieve webrtc-events subscription detailed information for a given + subscription. Including configuration data and current status. + operationId: retrieveNotificationChannelSubscription + security: + - openId: + - webrtc-events:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Webrtc-events Subscription + summary: "Delete a webrtc-events event subscription" + operationId: deleteNotificationChannelSubscription + description: | + API endpoint to delete a given webrtc-events subscription. Action done + to stop receiving notifications about this event subscription. + security: + - openId: + - webrtc-events:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: webrtc-events subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: |- + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + + Config: + description: |- + Implementation-specific configuration parameters needed by the subscription manager for acquiring + events. `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` are predefined for CAMARA + specifications. + + WebRTC specific event type attributes are included into `WebrtcSubscriptionDetail` schema. + + Note: if a request is performed for several event type, all subscribed event will use same `config` + parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/WebrtcSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: |- + The subscription expiration time (in date-time format) requested by the API consumer. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: |- + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + + Protocol: + type: string + enum: ["HTTP"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - ACCESSTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + required: + - credentialType + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + WebrtcSubscriptionDetail: + description: |- + The detail of the requested event subscription. + - org.camaraproject.webrtc-events.v0.session-invitation requires a + `deviceId` related to a valid registration. + - org.camaraproject.webrtc-events.v0.session-status requires a + `deviceId` related to a valid registration. + required: + - deviceId + properties: + deviceId: + type: string + format: uuid + description: |- + The device-id of the client in UUID format. A unique identifier for + the physical device where a registration is initiated. Generated + by the WebRTC application, and consistent within the same device. + + SubscriptionEventType: + type: string + description: |- + event-type - Event triggered when an event-type event occurred + - `org.camaraproject.webrtc-events.v0.session-status` + - Events triggered for any media session related event (e.g. far end new media endpoints) + - `org.camaraproject.webrtc-events.v0.session-invitation` + - Events triggered for any media endpoint registration event (e.g. incoming session) + - `org.camaraproject.webrtc-events.v0.registration-ends` + - Events triggered for registration termination (e.g. incoming session) + + `subscription-ended` is not supported for subscription. It is sent by default + enum: + - org.camaraproject.webrtc-events.v0.session-status + - org.camaraproject.webrtc-events.v0.session-invitation + - org.camaraproject.webrtc-events.v0.registration-ends + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: |- + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + RegistrationId: + type: string + description: The unique identifier of the WebRTC registration. + example: ln3C-ttOSk-ObcQ7A0-tYO1LXqy + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: |- + event-type that describes type of notification + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: |- + Event details payload. Depending of the event type, it will will include one of the data structures defined on this specification. Along with the subscription-ended, that is an authomatic event. + + Check the introduction documentation and the other CAMARA WebRTC APIs for extra info about data structures included on the events. + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.webrtc-events.v0.session-invitation: "#/components/schemas/EventSessionInvitation" + org.camaraproject.webrtc-events.v0.session-status: "#/components/schemas/EventSessionStatus" + org.camaraproject.webrtc-events.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + org.camaraproject.webrtc-events.v0.registration-ends: "#/components/schemas/EventRegistrationEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: |- + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + ############################################ + EventSessionInvitation: + description: |- + A `org.camaraproject.webrtc-events.v0.session-invitation` event includes an specific type of session + update for new requested sessions. It is emitted when the endpoint is associated with a valid + registration and the endpoint is susbcribed to recive new incoming calls. + + This event includes all the context information: caller, callee and possible carrier data to + contextualize (call subject, branding info, etc). It MUST include a mediaSessionId, to allow the + endpoint to subscribe to this new call session. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - data + properties: + data: + $ref: "#/components/schemas/MediaSessionInvite" + type: + enum: + - org.camaraproject.webrtc-events.v0.session-invitation + + ############################################ + EventSessionStatus: + description: |- + A `org.camaraproject.webrtc-events.v0.session-status` event includes the session updates provided by + the server. This will include actions form the endpoint and the server (far end). + + In general terms, it is received each time that an event happens within the session, and include + all relevant info about the session update. + + Most common use is for SDP updates and signaling updates regarding call status. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - mediaSessionId + - status + properties: + data: + $ref: "#/components/schemas/MediaSessionStatusUpdate" + type: + enum: + - org.camaraproject.webrtc-events.v0.session-status + + ############################################ + MediaSession: + description: |- + A prototype for media session infomration on Webrtc events. Used as event data schemas for session updates. + type: object + required: + - mediaSessionId + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + originatorAddress: + type: string + description: Sender (originator) address + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,})$' + example: 'tel:+11234567899' + originatorName: + type: string + description: Friendly name of the call originator + example: 'Alice' + receiverAddress: + type: string + description: Receiver (terminator) address + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,})$' + example: 'tel:+11234567899' + receiverName: + type: string + description: Friendly name of the call terminator + example: 'Bob' + status: + type: string + description: |- + Provides the status of the media session. During the session creation, + this attribute contains 'Initial' value + example: Initial + enum: + - Initial + - InProgress + - Ringing + - Proceeding + - Connected + - Terminated + - Hold + - Resume + - SessionCancelled + - Declined + - Failed + - Waiting + - NoAnswer + - NotReachable + - Busy + offer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + answer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + mediaSessionId: + type: string + description: The media session ID created by the network. The mediaSessionId shall not be included in POST requests by the client, but must be included in the notifications from the network to client. + example: '0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF' + reason: + type: string + description: The description of the event that has happened within the session + sequenceNumber: + type: integer + description: The sequence number of the notification sent to client + + MediaSessionStatusUpdate: + allOf: + - $ref: "#/components/schemas/MediaSession" + - type: object + description: MediaSession information emitted on a EventSessionStatus event + required: + - status + + MediaSessionInvite: + allOf: + - $ref: "#/components/schemas/MediaSession" + - type: object + description: MediaSession information emitted on a EventSessionInvitation event + required: + - originatorAddress + - receiverAddress + - status + + WrtcSDPDescriptor: + type: object + properties: + sdp: + type: string + description: |- + An inlined session description in SDP format [RFC4566].If XML syntax is used, the content of this element SHALL be embedded in a CDATA section + + # CloudEvent and CAMARA standard + EventSubscriptionEnded: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + type: + enum: + - org.camaraproject.webrtc-events.v0.subscription-ended + + SubscriptionEnded: + description: Event detail structure for SUBSCRIPTION_ENDED event + type: object + required: + - subscriptionId + - terminationReason + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: |- + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + # WebRTC Registration Ends event + EventRegistrationEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - data + properties: + data: + $ref: "#/components/schemas/RegistrationEnds" + type: + enum: + - org.camaraproject.webrtc-events.v0.registration-ends + + RegistrationEnds: + description: Event detail structure for REGISTRATION_ENDS event. registrationExpireTime is absolute UTC. Clients SHOULD refresh in advance; otherwise a REGISTRATION_EXPIRED terminationReason will be emitted. + type: object + required: + - registrationId + - terminationReason + properties: + registrationId: + $ref: "#/components/schemas/RegistrationId" + terminationDescription: + type: string + terminationReason: + $ref: "#/components/schemas/RegistrationTerminationReason" + + RegistrationTerminationReason: + type: string + description: |- + - NETWORK_TERMINATED - API server stopped sending notification + - REGISTRATION_EXPIRED - Registration expire time (optionally set by the requester) has been reached. REGISTRATION_EXPIRED is triggered exactly when the set registrationExpireTime has passed. + enum: + - NETWORK_TERMINATED + - REGISTRATION_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + GENERIC_422_MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED: + description: Combination of multiple event types is temporarily not supported + value: + status: 422 + code: MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED + message: The requested combination of event types is temporarily not supported. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + # Subscription examples + REGISTRATION_ENDS_SUBSCRIPTION: + description: |- + A sample of `registration-ends` subscription for registrationId + `+xsmcaum3z4zw4l0cu4w115m0` at `acme.opentelco.com`. + + This will be used to receive WebRTC registration termination events + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiL.." + accessTokenExpireUtc: "2024-12-06T14:37:56.147Z" + accessTokenType: "bearer" + types: + - org.camaraproject.webrtc-events.v0.registration-ends + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + INVITE_SUBSCRIPTION: + description: |- + A sample of media `session-invitation` subscription for phone number + `+1234567890` at `acme.opentelco.com`. + + This will be used to receive incoming sessions (incoming + calls). The implicit subscription to `subscription-ended` will make + the client aware of registration status updates from the server. + (i.e. when a REGISTRATION expires). + + The provided example will be able to receive up to 50 calls until + subscription is cancelled via server or by configuration timeout. Check + callback examples to check some possible events received: + + - New incoming call + - Registration revoked + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + types: + - org.camaraproject.webrtc-events.v0.session-invitation + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + initialEvent: true + subscriptionMaxEvents: 50 + subscriptionExpireTime: "2024-11-17T13:18:23.682Z" + SESSION_SUBSCRIPTION: + description: |- + A sample of media `session-status` subscription for a specific + `mediaSessionId` at `acme.opentelco.com`. + + Identified by for `mediaSessionId`, and validated via a `registrationId` + the endpoint is able to interact with its own media session. + This could be used to remotely control the call or to handle the async + session establishment. For instance, updating the user interface for + different statuses: InProgress, Ringing, Cancel, etc. + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + types: + - org.camaraproject.webrtc-events.v0.session-status + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + initialEvent: true + subscriptionMaxEvents: 50 + subscriptionExpireTime: "2024-11-17T13:18:23.682Z" + # Event examples + NEW_SESSION_INCOMING: + description: |- + Example of `session-invitation` event. + + A new media session is requested (i.e. incoming call). This event + starts a session negotiation. All other events related with this + media session will be shared via the `session-status` events, and + identified via the unique `mediaSessionId`. + + The main point to distinguish between a *new session* and an update over + an *existing session* is the **type**. A `session-invitation` describes + on its content, all information required to initiate a new voice-video call. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.session-invitation + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: "qs15-h556-rt89-1298" + originatorAddress: "tel:+11234567899" + originatorName: "Alice" + receiverAddress: "tel:+11234998765" + receiverName: "Bob" + status: "Initial" + offer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0" + mediaSessionId: "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" + reason: "New subscriber incoming call" + sequenceNumber: 1 + REGISTRATION_ENDS: + description: |- + Example of `registration-ends` events. + + This scenario occurs when the device did not refresh before the registration expiry time (registrationExpireTime). + When a re-registration is requested from server, maybe due to expire or + administrative token revocation or due any other technical reason. It + is expected from the endpoint to re-register. No new sessions will be + delivered to the user endpoint, as the subscription is not valid + anymore. + + Here, an example of how the network will communicate to the client that + the registration is not valid anymore, detailing on + `terminationDescription` the root cause of the registration removal. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.registration-ends + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: qs15-h556-rt89-1298 + registrationId: xsmcaum3z4zw4l0cu4w115m0 + terminationReason: REGISTRATION_EXPIRED + terminationDescription: "SIP re-registration required" + SESSION_UPDATE: + description: |- + Example of `session-status` events. + + Session status events are produced when there is an update on the + session status, due changes on the signaling status of the call (eg.: + InProgress, Ringing, Proceeding, Connected, Terminated, ...) or due + SDP changes on any involved party. + + This example, presents an SDP update due change on call status (to + Progress) and including answer SDP data. Customer client now, can + establish a voice-video channel and start transmitting and receiving + media. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.session-status + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: "qs15-h556-rt89-1298" + originatorAddress: "tel:+11234567899" + originatorName: "Alice" + receiverAddress: "tel:+11234998765" + receiverName: "Bob" + status: InProgress + offer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + mediaSessionId: "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" + reason: "Answer SDP update" + sequenceNumber: 3 + SUBSCRIPTION_ENDED: + description: |- + Example of `subscription-ended` events. + + Triggered when an event subscription is not valid anymore. Maybe due + administrative token revocation or due any other technical reason. It + is expected from the endpoint to subscribe again. No new events will be + delivered to the user endpoint, as the subscription is not valid + anymore. + + Here, an example of how the network will communicate to the client that + the subscription is not valid anymore, detailing on + `terminationDescription` the root cause of the subscription remove. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: qs15-h556-rt89-1298 + terminationReason: SUBSCRIPTION_EXPIRED + terminationDescription: "Subscription expired" +``` diff --git a/marked/WebRTC/code/API_definitions/webrtc-registration/raw.md b/marked/WebRTC/code/API_definitions/webrtc-registration/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..1ac10050cea79d0bf28b7aed1c0aa8f11718730e --- /dev/null +++ b/marked/WebRTC/code/API_definitions/webrtc-registration/raw.md @@ -0,0 +1,613 @@ +# webrtc-registration + +```yaml +openapi: 3.0.3 +info: + title: WebRTC Registration Service + description: |- + # Introduction + This API provides the API consumer with the capabilities to manage + registration and connectivity towards the network. + + The network requires that the API consumer application registers and + identifies an end user device before enabling any media + session services provided by the WebRTC APIs. + + A device registration created via this API will register a unique `deviceId` + created by the API consumer (WebRTC application) and it will will provide a + `registrationId` to manage a registration later. + Any subsequent request from the API consumer must include the unique + `registrationId` that will be linked to the registration previously defined. + + All operator network services are based on device registrations, this API + allows the user to create a registration session that enable the audio/video + functionalities exposed by the operator network. + + **Use cases to cover:** + - Functional: + - Ability to create Registration sessions on the network, this grants + access to create new audio and video sessions. + - Ability to update or remove Registration sessions on the network + - An additional subscription to webrtc-events API is required to receive + incoming calls. + + # Relevant terms and definitions + + - **registration** A media device session. A valid client running on a valid + device, with permission to use the network capabilities to create and receive + (audio/video) calls (media sessions). + - **registrationId**: Unique identifier of an WebRTC device **registration**. + Retrieved using the `webrtc-registration` API + - **deviceId**: A unique identifier for the physical device where a media + session is initiated. It is provided by the WebRTC application, it remains + consistent across multiple installations or logins on the same device. Its + primary function is to ensure that only one WebRTC session (**registration**) + is active per device at a time, enabling the gateway to clean up any stale + sessions if a new session is initiated on the same device. + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a Voice or Video **session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **x-correlator**: Unique ID included in the API request created by the API consumer. + It is used to correlate an API request with its response and help in debugging. + - **WebRTC**: WebRTC is a free and open-source project providing web browsers + and mobile applications with real-time communication via application programming + interfaces. It allows audio and video communication and streaming to work + inside web pages by allowing direct peer-to-peer communication + - **SDP**: Acronym for Session Description Protocol. The SDP is a format for + describing multimedia communication sessions for the purposes of announcement + and invitation. + + # API functionality + + This API allows to create device registrations. These, identified by a unique + `registrationId` can be updated and terminated via this API and its methods. + - **POST**: Create a new device registration using a valid authorization token. + - **PUT**: Update a device registration via its unique `registrationId` + - **DELETE**: Finish an existing device registration via its unique `registrationId` + To receive server-side updates about new voice-video sessions, you need to + use `webrtc-events` API. + + The main concept of the API is pretty straightforward: a subscriber needs a + session to create calls, so you will need a subscription on your device before + attempt any audio/video call. + + Once you create a session, you can: + - Use `webrtc-events` API to create a subscription and receive incoming calls. + - Use `webrtc-call-handling` API to create a audio/video session and create + an outgoing call. + + Check for extra details on each of these APIs already present on the WebRTC + repository. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.3.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: '{apiRoot}/webrtc-registration/v0.3' + description: APIs to manage device registration and connection + variables: + apiRoot: + description: API Root + default: http://localhost:9091 +tags: + - name: Registration + description: Operations to manage device registration with the network +paths: + /sessions: + post: + tags: + - Registration + summary: Create a registration + description: |- + API endpoint used to create a new registration of a device in the network. + It uses the `deviceId` in the request body. + In response, a `registrationId` (in UUID format) is provided to identify + this device registration within the network. + operationId: createRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - webrtc-registration:sessions:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionRequest' + responses: + '200': + description: Ok + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionResponse' + '400': + $ref: "#/components/responses/CreateSessionBadRequest400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/CreateSessionForbidden403" + /sessions/{registrationId}: + put: + tags: + - Registration + summary: Refresh network registration. + description: |- + API endpoint used to **refresh** an existing registration *before* it + expires. + + **Server behaviour on refresh** + + 1. Let `t_req` be the server-side receipt time of the request and + `t_prev` the previously stored `registrationExpireTime`. + 2. Compute the remaining lifetime + remaining = t_prev - t_req + (values ≤ 0 indicate the client is late; operators MAY reject or + treat it as a new registration). + 3. Apply the operator's configured TTL (`TTL_cfg`, e.g. 3600 s) **from + `t_req`, not from `t_prev`**: + newExpire = t_req + TTL_cfg + 4. Persist `newExpire` and return it in `expiresAt` inside the + response body. + + Clients SHOULD plan to refresh well **before** `newExpire` to avoid + race conditions. + operationId: updateRegistrationById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamRegistrationId' + security: + - openId: + - webrtc-registration:sessions:write + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionUpdate' + responses: + '200': + description: Ok + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionResponse' + '204': + description: Updated the registration status (no content) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: "#/components/responses/Generic400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/Generic403" + '404': + $ref: '#/components/responses/Generic404' + delete: + tags: + - Registration + summary: Delete Registration Session. + description: |- + API endpoint used to remove a valid registration on the network. This action + frees any resource and invalidates future actions that involves this + registration between the device and the network. + + Use the registrationId to identify the registration to delete. + operationId: deleteRegistrationById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamRegistrationId' + security: + - openId: + - webrtc-registration:sessions:delete + responses: + '204': + description: No Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: "#/components/responses/Generic400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/Generic403" + '404': + $ref: '#/components/responses/Generic404' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + pathParamRegistrationId: + name: registrationId + in: path + description: The registrationId assigned by the registration service + required: true + style: simple + explode: false + schema: + type: string + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + regSessionRequest: + type: object + required: + - deviceId + properties: + deviceId: + type: string + pattern: uuid + description: |- + The deviceId of the client in UUID format. A unique identifier for + the physical device where a registration is initiated. Generated + by the WebRTC application, and consistent within the same device. + registrationExpireTime: + type: string + format: date-time + description: |- + Optional **absolute** expiry moment for this registration. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + + ▸ **Devices without a trustworthy clock** (e.g. Wi-Fi-only tablets + or other non-SIM hardware) SHOULD treat the value as an + **upper bound**. Such devices MAY derive a local time-to-live: + + ttl = registrationExpireTime - now() + + and initiate a refresh *before* `ttl` elapses (a safety margin + of ~120 s is recommended). + + ▸ If the client omits this field, the server will set the expiry + according to its own TTL policy and return the resulting + `registrationExpireTime` in the response. + regSessionResponse: + type: object + required: + - registrationId + properties: + regInfo: + $ref: '#/components/schemas/RegistrationInformation' + registrationId: + type: string + description: The registration session ID is returned when registering a device with the network . Clients must utilize this ID to as a parameter in the call-handling and subscription APIs. + expiresAt: + type: string + format: date-time + description: |- + Authoritative expiry timestamp calculated **after** applying the + refresh logic. Clients MUST treat this value as the new upper-bound + and schedule their next refresh accordingly. + + Client applications should compute the remaining time before expiry (expiresAt - currentTime) + and plan to refresh well in advance to avoid race conditions. A suggested margin is 120 seconds before expiry. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + regSessionUpdate: + type: object + properties: + registrationExpireTime: + type: string + format: date-time + description: |- + Optional **absolute** UTC timestamp that *requests* a new expiry. + The server will honour the value only if it is **later than the + operator's minimum TTL** and **earlier than operator maximum TTL**; + otherwise it falls back to its own policy (see refresh algorithm + above). + + If omitted, the server always extends the expiry by its configured + TTL, measured from the moment the refresh is received. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + RegistrationStatus: + type: string + enum: + - Registered + RegistrationInformation: + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + regStatus: + $ref: '#/components/schemas/RegistrationStatus' + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represent + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + responses: + # Method specific responses + CreateSessionBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - EMERGENCY_ADDRESS_MISSING + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_EMERGENCY_ADDRESS_MISSING: + description: Specific Syntax Exception regarding emergency address that is relevant in the context of the API + value: + status: 400 + code: EMERGENCY_ADDRESS_MISSING + message: Emergency address missing + CreateSessionForbidden403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + - MAX_REGISTRATION_PER_USER + - MAX_REGISTRATION_PER_MSISDN + - MAX_DEVICES_PER_USER + examples: + CREATE_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + CREATE_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "device is not consistent with access token." + CREATE_403_MAX_REGISTRATION_PER_USER: + # summary: Max registration per user + value: + status: 403 + code: MAX_REGISTRATION_PER_USER + message: 'The maximum number of service registrations per user has been reached' + CREATE_403_MAX_REGISTRATION_PER_MSISDN: + # summary: Max registration per MSISDN + value: + status: 403 + code: MAX_REGISTRATION_PER_MSISDN + message: 'The maximum number of service registrations per MSISDN has been reached' + CREATE_403_MAX_DEVICES_PER_USER: + # summary: Max devices per user + value: + status: 403 + code: MAX_DEVICES_PER_USER + message: 'The maximum number of device instances per user has been reached' + # Generic responses + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. +``` diff --git a/marked/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist/raw.md b/marked/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..bf51ad90d98cf3cb921dc304bddce9d8313b3473 --- /dev/null +++ b/marked/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API WebRTC Call Handling + +Checklist for webrtc-call-handling v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-call-handling.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/marked/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist/raw.md b/marked/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..da39ded5e060ea2d0845234c3a24b5e73663e01e --- /dev/null +++ b/marked/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API WebRTC events + +Checklist for webrtc-events v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-events.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/marked/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist/raw.md b/marked/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..380130e6754a7dd90a06297599267f1f845f8b95 --- /dev/null +++ b/marked/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist/raw.md @@ -0,0 +1,19 @@ +# API WebRTC Registration + +Checklist for webrtc-registration v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                        public | stable
                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_231023/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_231023/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..b65d435dc26392fee375c204424fff363a4a3f3c --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_231023/raw.md @@ -0,0 +1,56 @@ +# MoM - WebRTC Working group - 231023 + +**Date:** 23/oct/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Cristina Santana (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santiago Troncoso (Quobis) +* Elías Pérez (Quobis) +* Jesus Pedruelo (Vodafone) +* Maxime Delon (Orange) + +## Agenda + +1. Welcome participants +2. Time slot approval +3. API Background +4. Scope definition: +
                                        • Technical Scope +
                                        • Task management
                                        +5. Roles definition (CODEOWNERS, MAINTAINERS) + + +## Discussion + +TMUS/Deepak : not to focus only on simple use cases and be concerned always that the API needs to be evolved to complex ones. +TMUS/Deepak : The current version of the API does not support choosing the line to be used for registration. It retrieves the MSISDN based on the deviceid provided by the client. The comment was to update the API to support selecting the line to be registered. +TMUS/Deepak : Notification channel – current version assumes websocket to be the only notification channel, the comment was to support multiple notification channel i.e. websocket, pns and web hooks. +Focus initially on the proposed use case to develop later - the initial version should be extensible to support any future changes. +The delivery UNI will initially be done thorugh JSON over websockets. +The NBI will be API REST. + +| Item | Who | Description | +| ---- | --- | ----------- | +| Time slot for the repetitions | webRTC WG| Aproved: Mondays 8am CET each 15 days. | +|Functional Scope aproval| webRTC WG| Aproved:
                                        Enable web endpoints (clients) to register, receive and make calls through an UNI API based on the OIDC FE flow. Then the functional scope for the API is:
                                        • Enable a web endpoint to register for IMS services through a webRTC Gateway using Oauth 2.0 and the Operator provided Identity Provider (IDP)
                                        • Open webSockets to receive IMS call events using JSON for the delivery
                                        • Make calls from the endpoint (client) side by establishing WebSocket using the channel URL received as part of the registration procedure.
                                        For this Scope two separated API are proposed:
                                        • One API for REST clients for 1-1 calling (CALL HANDLING)
                                        • One API for clients to manage Registration and Connectivity (RACM) towards MNO's IMS Network (REGISTRATION AND CONNECTIVITY MANAGEMENT)
                                        | +|Proposed Roles| webRTC WG | CODE OWNERS:
                                        • Ricardo Serrano: @TEF-RicardoSerr
                                        • Sushanth Hegde: @sushanthmavenir
                                        • Pradeep Achar Pushpa: @pradeepachar-mavenir
                                        MAINTAINERS:
                                        • Rafał Artych: @rartych
                                        • Deepak Jaiswal: @deepakjaiswal1
                                        • Santiago Troncoso: @stroncoso-quobis
                                        • Elías Pérez: @eliaspc
                                        • Jesus Pedruelo: @jesus-pb
                                        • Ratna Ratnanandan: @ratnavf
                                        • Benjamin Busvel: @BenjaminBusvel 
                                        | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Create the first PR with the two proposed seed YAML documents:
                                        • CallHandling-Service
                                        • RACM-Service| Ricardo Serrano| +| 2. Evaluate the accomodation of notifications to the webclient in the API Flow and bring a proposal for the nov/6th meeting | Sushanth Hegde | +| 3. Create a new issue "Notifications integration" to give ofline follow-up to Sushanth with his action point | Ricardo Serrano | +| 4. Update the repository information (maintainers, scope, codeowners etc.) | Ricardo Serrano | + +## AOB +* Next meeting will be the 6th of november diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_231106/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_231106/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37648537fd9f1438f711624bd2c2e73f9c710c5e --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_231106/raw.md @@ -0,0 +1,47 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 06/nov/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* David Moro (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Elías Pérez (Quobis) + +## Agenda + +1. Previous meeting minutes aproval +2. Notifications flow discussion +3. Identity providing + * Parameters handling (userID and deviceID) + * Line selection + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | Aproved | +| Notifications flow discussion | WebRTC WG | As stated in the previous meeting, there should be a third API specification file defined specifically for the Notification channel. Sushanth came up with the YAML specification and will be PR-ed by today.
                                          For now it only supports Websockets but in the future it may support other channel types.  | +| Parameters handling (userID and deviceID) | WebRTC WG | The userID will be the telco IdP token.
                                          The deviceID will be the unique device identifyer.
                                          • Regarding multitabs in browsers, there will not be provided new identities to each of the tabs as there will be multiple ringing (undesired behaviour) | +| Line selection | WebRTC WG | To close the issue as it is agreed that the line selection should be done outside the API scope.
                                            Anyhow, it is needed to see the end to end API to clarify this point | +| Error handling | WebRTC WG | Error handling should be taken into account and it need to be definded what to do in cases when the user do not have a line (error to be handled by the IdP) or state if there is needed to state a limit on registered lines for a user | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Close line selection issue opened | Ricardo Serrano | +| 2. Make the first contribution for the documentation of the API in markdown format | Sushanth Hegde | +| 3. Make the PR of the notification channel specification | Sushanth Hegde | +| 4. Make first proposal on Error Handling in the new Issue created | Deepak Jaiswal | +| 5. Review uploaded files on CAMARA, check the format and provide comments | All | + +## AOB + +* Next meeting will be the 20th of november diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_231120/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_231120/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..cc1826de8314c1d13dfd6d8c10c1ecacfec9e736 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_231120/raw.md @@ -0,0 +1,51 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 20/nov/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* David Moro (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santiago Troncoso (Quobis) +* Jesus Pedruelo (Vodafone) + +## Agenda + + +1. Previous meetings approval: Minutes of Meeting 231106 by TEF-RicardoSerr · [Pull Request #8](https://github.com/camaraproject/WebRTC/pull/8) · camaraproject/WebRTC · GitHub +2. Notification issue and PR comments discussion: Updated yaml files by pradeepachar-mavenir · [Pull Request #6](https://github.com/camaraproject/WebRTC/pull/6) · camaraproject/WebRTC · GitHub +3. Next steps (documentation) + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | To be Aproved | +| Notifications flow discussion | WebRTC WG |
                                            • T-Mobile sugests to keep the notification system method in a separate channel and only send to the API endpoint the content of the notification system. Also sugest to follow the OMA standard for API definition.
                                            • Telefonica concerns about PNS channels not being supported and the structure of the API itself.
                                            • Mavenir commit to update the YAMLs having this two bullets into account
                                            • The first sequence would be to create the notification channel and the second sequence would be to do the registration | +Others | WebRTC WG|
                                              • The operators have internal credentials which are the ones to be used in the registration process in the API (Telco IdP would provide the Token)
                                              • Quobis recommends making it clear in the documentation that the authentication process will be done via Oauth. | + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Error Analysis, [issue #7](https://github.com/camaraproject/WebRTC/issues/7) | Deepak Jaiswal| +| 2. Update the RACM and notificationchannel API so to be OMA compliant, and making sure that we can encapsule PNS in this new specification| Sushanth Hedge/ Padreep Achar | +| 4. Review and accept the previous minutes | Sushanth Hedge/ Padreep Achar | +| 5. Review uploaded files on CAMARA, check the format and provide comments | All | + +## AOB + +* Next meeting will be the *4th of December* + + +--------------------------------------------- + + + diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_231205/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_231205/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..707d8bb4ef61e561f4a7f1ab03047b18cb16932f --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_231205/raw.md @@ -0,0 +1,40 @@ +# MoM - WebRTC Working Group - 231205 + +**Date:** 5/dec/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Elías Pérez (Quobis) +* Benjamin Busvel (Orange) + +## Agenda + +1. Update on YAML files status: [Pull Request #6](https://github.com/camaraproject/WebRTC/pull/6) +2. Discussion current YAML files +3. Next Steps + + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Update on YAML files status | WebRTC WG| Mavenir have been doing some reviews and changes over the comments provided by the participants.| +|Discussion current YAML files| WebRTC WG| Documentation is ready and can be consulted:
                                              • [documentation/API_documentation/webrtc voice api.md](https://github.com/camaraproject/WebRTC/blob/main/documentation/API_documentation/webrtc%20voice%20api.md)
                                                Deepak (TMUS). Proposed changes to be discussed:
                                              • Incorporate the `notficationChannelURI` to the response in the RACM API
                                              • In the RACM API response, add support for multiple MSISDN users (add `msisdn` param (list of MSISDNs the user have launched the service in) within the `connectionInformation` schema as optional). Also add the proper error codes to support this. | +|Next steps| webRTC WG | It is proposed to incorporate the minor changes proposed during the meeting and come up with the first release of the API (version 0.1.0)
                                                For the next release of the API (version 0.1.1) it is proposed to incorporate the handling of multilines-users in the RACM API (depending on complexity this could be incorporated in this release but only for the responses) | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review the pull request regarding format and update of the repository proposed by Ricardo | Pradeep Achar | +| 2. Review minor changes proposed by Deepak and try to acomodate them | Pradeep Achar | +| 3. Propose commented changes over ther existing Pull Request if needed | Deepak Jaiswal | +| 4. Merge the PR and come up with the first release of the API once all the changes are ready | Ricardo Serrano | +| 5. Review all the repository contributions and provide comments (do not hessitate to open a new issue or a PR if you consider it necessary) | All | + +## AOB +* Next meeting will be the 19th of december diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_231219/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_231219/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f3caa8321d4698cf5a4660372551a3e142af8a3d --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_231219/raw.md @@ -0,0 +1,51 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 19/dec/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) + + +## Agenda + + +1. Comments about first release (0.1). First version of the API. +2. Diferents comments about the API + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | To be Aproved | +| Sucessfull first Api version | WebRTC WG | First version of the API aproval and complete.| +| More aplications for the API | T- Mobile | Propose to develope new features for the API. It is important to implement this first version on the API before looking forward for new funcionalities. It is necesarry to push for the massive adoption that we are looking for.| +CAMARA alignment | T -Mobile | Alignment the API definitions with the CAMARA guidelines (CAMARA falvour) + + + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Check internally new features for the API | all| +| 2. T-Mobile is interested in deploy the API and Telefonica discuss internally | T-Mobile / TEF| +| 3. Review the definitions and alignment with CAMARA guidelines | Ricardo (TEF) | + + + +## AOB + +* Next meeting will be the *16 th of January* + + +--------------------------------------------- + diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_240116/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_240116/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..2df565781730f7ca3b60c88041a83a6fac787647 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_240116/raw.md @@ -0,0 +1,47 @@ +# MoM - WebRTC Working group - 240116 + +**Date:** 16/Jan/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Deepak Jaiswal (T-Mobile US) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Delon Maxime (Orange) +* Santi Troncoso (Quobis) +* Jesus Pedruelo (Vodafone) + + +## Agenda + +1.WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Comments about general issues commented by Benjamin
                                                1. Review GET status session and look if is mandatory
                                                2. Documentation to clarify who use the API
                                                3. Change status when create a session, the status must not be entered
                                                4. Create a specific yaml file for notification | Orange | Summarize in a pull request all coments did by Benjamin +| Commiting to implement API? | Telefonica
                                                  Orange
                                                  Vodafone
                                                  | Commited to implement but there is not a implementation plan in short time scope | + +In general: Recap all the issues and make and example thorugh a PR in order to diiscuss over this. + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Check internally new features for the API | all | +| 2. Recap all the issues comented in a pull request | Delon/Benjamin (Orange)| +| 3. Documentation and flows API usage | Santi Troncoso (Quobis) & Ricardo Serrano (Telefonica) | + + +## AOB + +* Next meeting will be the *30th of January* + + +--------------------------------------------- diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_240130/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_240130/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..57fb1dbbadff208e017b0aacbb66ae7879a585e6 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_240130/raw.md @@ -0,0 +1,45 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 30/Jan/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile USA) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santi Troncoso (Quobis) + + + +## Agenda + +WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Emergency calls | Deepak | As it is a call service, it is mandatory to establish the emergency call service. Emergency parameters should be within the rest of the API params. Location could be an additional/optional parameter. It is good that location parameter will be inside de API parameters to support emergency call service.| +|Issue 2: Update BYON flow doc | Ricardo
                                                  Javier
                                                  Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                  Add autonumbers in the UML format +|Issue 3: Review API response | Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Correct the documentation BYON flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25)| all | +| 5. PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | + +## AOB + +* Next meeting will be the *13rd of February* + diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_240213/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_240213/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ce1472de92714f13a96aff0d56a1577d3857cf33 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_240213/raw.md @@ -0,0 +1,46 @@ +# MoM - WebRTC Working group - 240213 + +**Date:** 13/Feb/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (Deutsche Telekom) +* Deepak Jaiswal (T-Mobile USA) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) + + + +## Agenda + +WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Emergency calls | Ricardo and Deepak | Location feature to be stablished at the Operator Network not in GateWay.
                                                  ¿It is optional to provide a location parameter? YES.
                                                  Get the location in this device model (not tipical mobile device) could be more difficult. It doesnt have location capabilities (such as GPS, or cellular location).
                                                  If no location provided user might need to provide it and maybe store it in a separate file to be consulted.| +|Issue 2: Update BYON flow doc | Ricardo
                                                  Javier
                                                  Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                  Add autonumbers in the UML format +|Issue 3: Review API response | Ricardo and Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) +|Issue 5: RACM Session |Deepak | Change session names because some session id names may lead into confusion and URL return - Session id | + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Correct the documentation BYON flow. PUT response to RACH. Make a proposal to change [PR#21](https://github.com/camaraproject/WebRTC/pull/21)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25)| all | +| 5. PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | +|6. RACM session names Pull Request and url to SessionId |Deepak + +## AOB + + * Next meeting will be the *27th of February* \ No newline at end of file diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_240227/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_240227/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f1e36e28ddb36a07151df5440492b93379336c1c --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_240227/raw.md @@ -0,0 +1,43 @@ +# MoM - WebRTC Working group - 240227 + +**Date:** 27/Feb/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (Deutsche Telekom) +* Deepak Jaiswal (T-Mobile USA) +* Santiago Troncoso (Quobis) + + + +## Agenda + +WebRTC working group CAMARA Meeting. Review the diferrents Pull Request + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Update BYON-CallHandling Session | Ricardo and Javier | Reviwed and updated the BYON-CallHandling code. Add 201 (created) response as indicated in HTTP guidelines for a 201 in the PUT session .| +|Issue 2: Update BYON flow doc | Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                  Add autonumbers in the UML format. Review the updated flow doc. Suggest to close the last doc open by Javier and continue with the new one. Separate the doc in two files. +|Issue 3: Review API response | Ricardo and Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24). Fix description and provide some samples for the clarification. Provide a sample in POST too +|Issue 4: RACM Session |Deepak | Change session names because some session id names may lead into confusion and URL return -> Session id.
                                                  The idea is not to create different channels as an app so to the Web RTC gateway we provide this channel and the Web RTC would deliver this notification to this notification channel either using the web book. If the webook web RTC is aware internally about the channel it could use the ID and get how to deliver to the channel. PNS to be explored | + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#27](https://github.com/camaraproject/WebRTC/pull/27) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Keep on working in call flow. To be added some missing arrows. [PR#27](https://github.com/camaraproject/WebRTC/pull/27)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25) | all | +| 5. Correct 201 response (status) [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | +| 6. RACM session names Pull Request and url to SessionId [PR#29](https://github.com/camaraproject/WebRTC/pull/27) | Deepak | + +## AOB + + * Next meeting will be the *12th of March* + diff --git a/marked/WebRTC/documentation/MeetingMinutes/MoM_240312/raw.md b/marked/WebRTC/documentation/MeetingMinutes/MoM_240312/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..7019bc25469ab349b8b353005e0606f02f987ca0 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/MoM_240312/raw.md @@ -0,0 +1,48 @@ +# MoM - WebRTC Working group - 240312 + +**Date:** 12/March/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile USA) +* Santiago Troncoso (Quobis) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Bhabani (Meta) + + + + +## Agenda + +WebRTC working group CAMARA Meeting. Review the diferrents Pull Request + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Update BYO-CallHandling Session | Ricardo and Javier | Updated the BYON-CallHandling code. Update .yaml Gereric201
                                                  from: $ref: '#/components/schemas/ObjectResponse'
                                                  To: $ref: '#/components/schemas/ReceiverSessionStatus'
                                                  [PR#28](https://github.com/camaraproject/WebRTC/pull/28)| +|Issue 2: Update BYON flow doc | Santiago | [Issue#15](https://github.com/camaraproject/WebRTC/issues/15) and [Issue#17](https://github.com/camaraproject/WebRTC/issues/17) Added some missing arrows. Work in progress Separate the doc in two files, Include a simple description of the events in API, and improvement the notification documentation. Add more clarity and action bars. +|Issue 3: RACM Session |Deepak |Updated three yamls files. The primary change in the RACM API is the session ID parameter.
                                                  Include additional channel types (Eg:PNS) and change the resource URL to a channel ID. | + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Upload commit to WebRTC repository with updated Update .yaml Gereric201 | Ricardo and Javier| +| 2. Finish the flow documentation and upload to Camara Github group |Santiago| +| 3. Review changes proposed by Deepack |Sushanth| +| 4. Aproval the minutes and comments if necessary [#PR11](https://github.com/camaraproject/WebRTC/pull/11) and [#PR30](https://github.com/camaraproject/WebRTC/pull/30) | Deepack and Sushanth| + +## AOB + + * Next meeting will be the *26th of March* + * From then to now the minutes will be uploaded to [Confluence](https://wiki.camaraproject.org/display/CAM/Minutes) + +--------- \ No newline at end of file diff --git a/marked/WebRTC/documentation/MeetingMinutes/README/raw.md b/marked/WebRTC/documentation/MeetingMinutes/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..5bde81e30f827dc7b5205f19c5b521dbee983de8 --- /dev/null +++ b/marked/WebRTC/documentation/MeetingMinutes/README/raw.md @@ -0,0 +1,5 @@ +# Meeting notes + +These meetings notes are stored her for archive purposes, find updated Meeting notes at CAMARA main Wiki website + +* https://wiki.camaraproject.org/display/CAM/WebRTC+Meeting+Minutes diff --git a/marked/WebRTC/documentation/README/raw.md b/marked/WebRTC/documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..dee80b0282e6d598dd6fcbcef853df0374038801 --- /dev/null +++ b/marked/WebRTC/documentation/README/raw.md @@ -0,0 +1,13 @@ +# Documentation + +This folder include extra documentation about the API beyond the technical OpenAPI v3 API description of the `code` folder + +* [MeetingMinutes](MeetingMinutes/) + * Check this folder for the original meeting minutes. + * Newer meeting minutes can be found at [CAMARA Wiki](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564608/WebRTC+Meeting+Minutes) + +* [API_documentation](API_documentation/) + * Check this folder for release status documentation. + +* [SupportingDocuments](SupportingDocuments/) + * Check this folder for extra documentation to support the API definition, UML activity diagrams, API overview description, how to use guides, and other documentation related.. diff --git a/marked/WebRTC/documentation/SupportingDocuments/README/raw.md b/marked/WebRTC/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..8b478fa31a6bf84a679023c122683fb32e88116e --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1,12 @@ +# Supporting documents + +This folder include documentation to support the API definition, API overview description, how to use guides, and other documentation related with the OpenAPI v3 specs of the `API_definitions` folder. + +* [UML diagrams](uml-diagrams/) + * Check the UML diagrams included for the documented use cases. They include UML activity diagrams that depict a detailed interaction between apps, WebRTC GW and IMS network. + +* [WebRTC voice API](webrtc%20voice%20api.md) + * Check this document for introduction to the API, and brief expanation of the API itself, use cases and status descriptions. + +* [Obtaining a WebRTC SDP to create calls](webrtc-call-handling-sdp-gathering.md) + * CAMARA `webrtc-call-handling` API requires basic usage of the WebRTC API to create calls. You need to obtain and create an `SDP`(Session Description Protocol) body to use in the call creation. This document review that process. diff --git a/marked/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW/raw.md b/marked/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..46658c2155c0dd5bcc2a2833342c12129f3f3be1 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW/raw.md @@ -0,0 +1,12 @@ +# WebRTC API User Story (Inbound-Outbound calling: ASP-WebRTC Gateway scenario) + +| **Item** | **Details** | +| --- | --- | +| ***Summary*** | As a web application developer, I want to develop and provide a WebRTC application through an Application Service Provider that enables end users to make and receive calls (outbound and inbound) over the internet using carrier phone numbers.| +| ***Actors and Scope*** | **Actors:** Device Application, Application Servers (API Consumer), Auth Server, WebRTC Gateway (API Provider), Telco Network, Remote Endpoint.
                                                  **Scope:**
                                                  • Outbound calls: Initiate calls to Remote Endpoints in the Telco Network using phone numbers and establish media sessions.
                                                  • Inbound calls: Receive calls from Remote Endpoints in the Telco Network using phone numbers and establish media sessions.
                                                  | +| ***Pre-conditions*** | The preconditions are listed below:
                                                  • **Device Application:**
                                                    • Provided to end users from the Application Service Provider's Application Servers.
                                                    • Users are authenticated by the Application Servers provided by the Application Service Provider, and the Device Application and Application Servers are connected via a secure communication channel.
                                                  • **Application Servers:**
                                                    • Operated by the Application Service Provider and functions as a WebRTC API Consumer. Makes requests to the WebRTC Gateway in response to Device Application requests. Notifications from the WebRTC Gateway to the Application Servers are relayed to specific Device Applications based on their content.
                                                    • Authenticates Device Application users with proprietary service IDs and credentials. The connection between Application Servers and Device Applications is protected by a secure communication channel. As a result of end user consent through authentication and authorization using the communication carrier account, tokens for requesting the WebRTC API in response to Device Application requests are issued by the communication carrier.
                                                  • **Auth Server:**
                                                    • An authentication and authorization server operated by the communication carrier that manages the association between end users utilizing the Device Application and the phone numbers available to those users.
                                                    • Performs end user authentication, authorization, and consent using communication carrier accounts, and tokens are issued to Application Servers for accessing the WebRTC API.
                                                  • **WebRTC Gateway:**
                                                    • A server operated by the carrier that functions as the WebRTC API provider which validates API requests from Application Servers using the Auth Server and provides registration enabling calls using end user phone numbers, call event notifications, and interworking functionality to the Telco Network.
                                                  • **Telco Network:**
                                                    • The communication carrier's telephony service network, connected to the WebRTC Gateway.
                                                  • **Remote Endpoint:**
                                                    • An endpoint capable of using the communication carrier's telephony service, connected to and registered with the Telco Network.

                                                  See below figure. | +| ***Activities/Steps*** | **Starts when:** In response to a Device Application request, the Application Server prepares to establish a media session with the WebRTC Gateway.

                                                  **Step 1:** The Application Server configures event notification subscriptions with the WebRTC Gateway for call state changes and incoming calls for each Device Application.

                                                  **Step 2:** The Application Server performs registration with the WebRTC Gateway to enable outbound-call and inbound-call for each Device Application. At this time, the phone number to be used is presented to the Application Server by the WebRTC Gateway.

                                                  **Step 3a:** (When the Device Application initiates an outbound-call) In response to a Device Application request, the Application Server sends a media session establishment request to the WebRTC Gateway, specifying the originating and terminating phone numbers. The WebRTC Gateway validates the requested phone numbers and interworks the session establishment request to the Telco Network, while responses from the Telco Network are sent to the Application Server as interworking result event notifications. Once the necessary negotiation is completed, a media session is established between the Device Application and the Remote Endpoint.

                                                  **Step 3b:** (When the Device Application receives an inbound-call) When an incoming call arrives from the Telco Network, the WebRTC Gateway sends an incoming call event notification to the Application Server. The Application Server retrieves detailed call information from the WebRTC Gateway and performs the necessary negotiation to establish the media session. Once the necessary negotiation is completed, a media session is established between the Device Application and the Remote Endpoint.

                                                  **Ends when:** A call media session is established between the Device Application and the Remote Endpoint.| +| ***Post-conditions*** | When media session state changes (e.g., media modifications) or registration expiration occurs, the WebRTC Gateway sends event notifications to the Application Server, and actions such as renegotiation or registration refresh are performed. The media session terminates when disconnected by either the Device Application or the Remote Endpoint.| +| ***Exceptions*** | Several exceptions might occur during the WebRTC API operations:
                                                  - Unauthorized: Invalid credentials (e.g., expired access token).
                                                  - Incorrect input data (e.g., malformed phone number).
                                                  - Not able to provide: Appropriate event subscriptions and registration have not been performed by the Application Server to initiate outbound-calls or enable inbound-calls reception.| +--- +![fig](./images/fig_user_story_scenario2.png) \ No newline at end of file diff --git a/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README/raw.md b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..88e816bd595d3b0d08ed264efdcb585c2893c277 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README/raw.md @@ -0,0 +1,34 @@ +# WebRTC API call flows + +## 1. General + +This document provides example call flows and messages based on WebRTC API user story for implementers of a WebRTC Gateway that exposes WebRTC APIs and interworks with telco network. + +## 2. Actors + +The involved actors in the call flows are as follows: + +- **Device Application**:A native application or web application running on the user’s device. + +- **Application Server**: Acts as a WebRTC API Invoker. + +- **Auth Server**: Performs auth for API usage in accordance with the CAMARA ICM specification. + +- **WebRTC Gateway**: Acts as a WebRTC API provider, and also interworks with telco network. + +- **Telco Network**: Acts as signalling (SIP) & media servers. + +- **Remote Endpoint**:The peer in the call using the WebRTC API. + + +## 3. List of call flow examples + +The following links provide call flow diagrams and message examples. + +- 3.1. [Subscription for WebRTC events](./subscription_for_webrtc_events.md) +- 3.2. [WebRTC registration](./webrtc_registration.md) +- 3.3. [Call orignation and disconnection](./call_origination_and_disconnection.md) +- 3.4. Call termination and disconnection (TBD) + +The message examples illustrate the fields necessary for implementing a WebRTC Gateway, including all defined optional fields where applicable. +Although the API specification defines fields for [API-design-guidline](https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md) consistency, those not applicable in the WebRTC API are excluded from the message examples. diff --git a/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection/raw.md b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..711e14e4d8b2c1d6e99f8950bee790576cfaf5a7 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection/raw.md @@ -0,0 +1,506 @@ +# 3.3. Call origination and disconnection + +This part of the call flows cover call origination from Application Server as WebRTC API Invoker. + +In the call flows, the interface between the WebRTC Gateway and the Telco Network is a SIP-based NNI (Network-to-Network Interface). As such, IMS access-layer procedures (e.g., resource reservation, precondition) are out of scope, while reliable provisional responses (100rel / PRACK) are assumed to be supported on the NNI. + +## 3.3.1. Call origination +### 3.3.1.1. Call flow + +![fig1](./call_origination_and_disconnection_fig-1.png) + +### 3.3.1.2. Example messages + +#### [7] POST /webrtc-call-handling/v0.3/sessions +```http +POST /webrtc-call-handling/v0.3/sessions HTTP/1.1 +Host: webrtc-gw.operator.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000007 +registrationId: reg-550e8400-e29b-41d4-a716-446655440000 + +{ + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + } +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #147 +> +> Related PR: #NN +> +> The current API definition uses a single MediaSessionInformation schema as the message body across multiple operations (POST request/response, GET response, and PUT request/response). However, the set of required properties varies depending on the operation context. This overloading of a single schema reduces clarity and may lead to ambiguity for API consumers regarding which fields are mandatory in each operation. +> +> It is proposed to define distinct schema types corresponding to each operation context (e.g., CreateMediaSessionRequest, CreateMediaSessionResponse, MediaSessionInfo, UpdateMediaSessionRequest, UpdateMediaSessionResponse) in webrtc-callhandling.yaml, and update the $ref references in each operation accordingly. + + +#### [10] SIP INVITE +``` +INVITE sip:+818000000002@tn.operator.com;user=phone SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Supported: 100rel, timer +Allow: INVITE, ACK, BYE, CANCEL, UPDATE, PRACK, OPTIONS +Content-Type: application/sdp +Content-Length: 266 + +v=0 +o=- 8066321617929821805 2 IN IP4 webrtc-gw.operator.com +s=WebRTC-to-SIP Call +c=IN IP4 203.0.113.100 +t=0 0 +m=audio 30000 RTP/AVP 0 8 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:8 PCMA/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [13] SIP 100 Trying +``` +SIP/2.0 100 Trying +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Content-Length: 0 +``` + +#### [14] 201 Created +```http +HTTP/1.1 201 Created +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000007 + +{ + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Initial", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" +} +``` + +#### [17] SIP 183 Session Progress +``` +SIP/2.0 183 Session Progress +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Require: 100rel +RSeq: 1 +Content-Type: application/sdp +Content-Length: 223 + +v=0 +o=- 4576312012535546667 2 IN IP4 198.51.100.10 +s=SIP Call +c=IN IP4 198.51.100.10 +t=0 0 +m=audio 49170 RTP/AVP 0 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [18] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000016 + +{ + "id": "evt-183-f47ac10b-58cc-4372-a567-0e02b2c3d479", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:01.123Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "InProgress", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "answer": { + "sdp": "v=0\r\no=- 7893214567890123456 2 IN IP4 203.0.113.100\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\nm=audio 50000 UDP/TLS/RTP/SAVPF 111\r\nc=IN IP4 203.0.113.100\r\na=candidate:2098703421 1 udp 2122262783 203.0.113.100 50000 typ host generation 0\r\na=ice-ufrag:B7nX\r\na=ice-pwd:m9sK3jLpQwErT6yHvC2xNfAz\r\na=fingerprint:sha-256 A1:B2:C3:D4:E5:F6:07:18:29:3A:4B:5C:6D:7E:8F:90:01:12:23:34:45:56:67:78:89:9A:AB:BC:CD:DE:EF:F0\r\na=setup:active\r\na=mid:0\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\n" + }, + "reason": "183 Session Progress received from remote endpoint", + "sequenceNumber": 1 + } +} +``` + +#### [20] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000016 +``` + +#### [21] SIP PRACK +``` +PRACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 2 PRACK +RAck: 1 1 INVITE +Content-Length: 0 +``` + +#### [24] SIP 200 OK (PRACK) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack1;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 2 PRACK +Content-Length: 0 +``` + +#### [30] SIP 180 Ringing +``` +SIP/2.0 180 Ringing +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Require: 100rel +RSeq: 2 +Content-Length: 0 +``` + +#### [31] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000027 + +{ + "id": "evt-180-a8b9c0d1-e2f3-4456-b789-0a1b2c3d4e5f", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:02.456Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Ringing", + "reason": "180 Ringing received from remote endpoint", + "sequenceNumber": 2 + } +} +``` + +#### [33] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000027 +``` + +#### [34] SIP PRACK +``` +PRACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack2 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 3 PRACK +RAck: 2 1 INVITE +Content-Length: 0 +``` + +#### [37] SIP 200 OK (PRACK) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack2;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 3 PRACK +Content-Length: 0 +``` + +#### [39] SIP 200 OK (INVITE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Allow: INVITE, ACK, BYE, CANCEL, UPDATE, PRACK, OPTIONS +Supported: 100rel, timer +Content-Type: application/sdp +Content-Length: 223 + +v=0 +o=- 4576312012535546667 4 IN IP4 198.51.100.10 +s=SIP Call +c=IN IP4 198.51.100.10 +t=0 0 +m=audio 49170 RTP/AVP 0 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [40] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000035 + +{ + "id": "evt-200-c4d5e6f7-8901-2345-6789-abcdef012345", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:05.789Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Connected", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "answer": { + "sdp": "v=0\r\no=- 7893214567890123456 4 IN IP4 203.0.113.100\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\nm=audio 50000 UDP/TLS/RTP/SAVPF 111\r\nc=IN IP4 203.0.113.100\r\na=candidate:2098703421 1 udp 2122262783 203.0.113.100 50000 typ host generation 0\r\na=ice-ufrag:B7nX\r\na=ice-pwd:m9sK3jLpQwErT6yHvC2xNfAz\r\na=fingerprint:sha-256 A1:B2:C3:D4:E5:F6:07:18:29:3A:4B:5C:6D:7E:8F:90:01:12:23:34:45:56:67:78:89:9A:AB:BC:CD:DE:EF:F0\r\na=setup:active\r\na=mid:0\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\n" + }, + "reason": "200 OK received - call connected", + "sequenceNumber": 3 + } +} +``` + +#### [42] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000035 +``` + +#### [43] SIP ACK +``` +ACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776ack1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 ACK +Content-Length: 0 +``` + + + + + + + +## 3.3.2. Call termination by call originator +### 3.3.2.1. Sequence + +![fig2](./call_origination_and_disconnection_fig-2.png) + +### 3.3.2.2. Example messages + +#### [53] DELETE /webrtc-call-handling/v0.3/sessions/{mediaSessionId} +```http +DELETE /webrtc-call-handling/v0.3/sessions/0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF HTTP/1.1 +Host: webrtc-gw.operator.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000051 +``` + +#### [56] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000051 +``` + +#### [57] SIP BYE +``` +BYE sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776bye1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 4 BYE +Content-Length: 0 +``` + +#### [60] SIP 200 OK (BYE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776bye1;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 4 BYE +Content-Length: 0 +``` + +#### [61] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000059 + +{ + "id": "evt-bye-d5e6f7a8-b901-2345-6789-abcdef012345", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:35:00.123Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Terminated", + "reason": "Call terminated by originator", + "sequenceNumber": 4 + } +} +``` + +#### [63] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000059 +``` + +## 3.3.3. Call termination by call receiver +### 3.3.3.1. Sequence + +![fig3](./call_origination_and_disconnection_fig-3.png) + +### 3.3.3.2. Example messages + +#### [48] SIP BYE +``` +BYE sip:webrtc-gw.operator.com:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP 198.51.100.10:5060;branch=z9hG4bK889bye1 +Max-Forwards: 70 +From: ;tag=a6c85cf +To: "Alice" ;tag=1928301774 +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 BYE +Content-Length: 0 +``` + +#### [49] SIP 200 OK (BYE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP 198.51.100.10:5060;branch=z9hG4bK889bye1;received=198.51.100.10 +From: ;tag=a6c85cf +To: "Alice" ;tag=1928301774 +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 BYE +Content-Length: 0 +``` + +#### [51] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000049 + +{ + "id": "evt-bye-e6f7a8b9-c012-3456-7890-abcdef123456", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:35:00.456Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Terminated", + "reason": "Call terminated by receiver", + "sequenceNumber": 4 + } +} +``` + +#### [53] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000049 +``` + + + + + + + + + diff --git a/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events/raw.md b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..d96fb7f8fe50a8a19a18f63508f6ef57ab5527f9 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events/raw.md @@ -0,0 +1,267 @@ +# 3.1. Subscription for WebRTC events + +This part of the call flow covers subscribing, unsubscribing, and updating subscriptions for WebRTC events. + +## 3.1.1. Event Subscriptions +### 3.1.1.1. Sequence + +![fig1](./subscription_for_webrtc_events_fig-1.png) + +### 3.1.1.2. Example messages +#### [3] GET /authorize +``` +GET /authorize?response_type=code + &client_id=asp-webrtc-app-001 + &redirect_uri=https%3A%2F%2Fasp.example.com%2Fcallback + &scope=openid%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.session-invitation%3Acreate%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.session-status%3Acreate%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.registration-ends%3Acreate + &state=af0ifjsldkj + &code_challenge=E9Melhoa2OwvFrEMTJguCHaoeK1t8URWbuGJSstw-cM + &code_challenge_method=S256 HTTP/1.1 +Host: auth.operator.com +``` + +#### [4] 302 Found +``` +HTTP/1.1 302 Found +Location: https://asp.example.com/callback?code=SplxlOBeZQQYbYS6WxSbIA&state=af0ifjsldkj +``` + +#### [6] POST /token +``` +POST /token HTTP/1.1 +Host: auth.operator.com +Content-Type: application/x-www-form-urlencoded + +grant_type=authorization_code +&code=SplxlOBeZQQYbYS6WxSbIA +&redirect_uri=https%3A%2F%2Fasp.example.com%2Fcallback +&code_verifier=dBjftJeZ4CVP-mB92K27uhbUJU1p1r_wW1gFWFOEjXk +``` + +#### [7] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +Cache-Control: no-store + +{ + "access_token": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9.eyJpc3MiOiJodHRwczovL2F1dGgub3BlcmF0b3IuY29tIiwic3ViIjoiKzEyMzQ1Njc4OTAiLCJhdWQiOiJhc3Atd2VicnRjLWFwcC0wMDEiLCJleHAiOjE3MzQyNzI2MDAsImlhdCI6MTczNDI2OTAwMCwic2NvcGUiOiJvcGVuaWQgd2VicnRjLWV2ZW50czpvcmcuY2FtYXJhcHJvamVjdC53ZWJydGMtZXZlbnRzLnYwLnNlc3Npb24taW52aXRhdGlvbjpjcmVhdGUgd2VicnRjLWV2ZW50czpvcmcuY2FtYXJhcHJvamVjdC53ZWJydGMtZXZlbnRzLnYwLnNlc3Npb24tc3RhdHVzOmNyZWF0ZSB3ZWJydGMtZXZlbnRzOm9yZy5jYW1hcmFwcm9qZWN0LndlYnJ0Yy1ldmVudHMudjAucmVnaXN0cmF0aW9uLWVuZHM6Y3JlYXRlIn0.signature", + "token_type": "Bearer", + "expires_in": 3600, + "refresh_token": "tGzv3JOkF0XG5Qx2TlKWIA", + "id_token": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9.eyJpc3MiOiJodHRwczovL2F1dGgub3BlcmF0b3IuY29tIiwic3ViIjoiYWJjZDEyMzQiLCJhdWQiOiJhc3Atd2VicnRjLWFwcC0wMDEiLCJleHAiOjE3MzQyNzI2MDAsImlhdCI6MTczNDI2OTAwMCwibm9uY2UiOiJuLTBTNl9XekEyTWoifQ.signature" +} +``` + +#### [8] POST /webrtc-events-suscription/{apiVersion}/subscriptions +``` +POST /webrtc-events/v0.2/subscriptions HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: b4333c46-49c0-4f62-80d7-f0ef930f1c46 + +{ + "protocol": "HTTP", + "sink": "https://asp.example.com/webhooks/webrtc", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.abc123", + "accessTokenExpiresUtc": "2025-12-20T23:59:59.999Z", + "accessTokenType": "bearer" + }, + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2025-12-31T23:59:59.999Z" + } +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #135 +> +> Related PR: #NN +> +> Per the updated CAMARA-API-Event-Subscription-and-Notification-Guide.md, event subscriptions (`session-invitation`, `session-status`, `registration-ends`) are consolidated into a single request using the types array to reduce transactions. +> +> This consolidated subscription pattern should be reflected in the webrtc-events.yaml examples. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #76 +> +> Related PR: #NN +> +> The following fields (derived from CAMARA-API-Event-Subscription-and-Notification-Guide) are omitted as they are not applicable to WebRTC events: +> - `subscriptionMaxEvents`: The number of events generated by the WebRTC API cannot be predicted in typical use cases. For resource lifecycle management, `subscriptionExpireTime` is the recommended approach. +> - `initialEvent`: None of the WebRTC events (`session-status`, `session-invitation`, `registration-ends`) are triggered at the event subscription. +> +> Informational descriptions for above fields need to be added in webrtc-events.yaml. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #136 +> +> Related PR: #NN +> +> The webrtc-events.yaml states that `HTTPSubscriptionRequest` and `HTTPSubscriptionResponse` schemas are applied when the `proto` field value is "HTTP", but the current examples do not reflect those schemas. +> +> It should be clarified whether to: +> - Update the examples to conform to the specification, or +> - Remove the schemas above. + +#### [11] 201 Created +``` +HTTP/1.1 201 Created +Content-Type: application/json +x-correlator: b4333c46-49c0-4f62-80d7-f0ef930f1c46 + +{ + "protocol": "HTTP", + "sink": "https://notificationServer.example.com/webhooks/webrtc", + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2025-12-31T23:59:59.999Z" + }, + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "startsAt": "2025-12-15T10:30:00.000Z", + "expiresAt": "2025-12-31T23:59:59.999Z", + "status": "ACTIVE" +} +``` + +## 3.1.2. Refresh event subscriptions +### 3.1.2.1. Sequence + +![fig1](./subscription_for_webrtc_events_fig-2.png) + +### 3.1.2.2. Example messages +#### [18] PUT /webrtc-events-suscription/{apiVersion}/subscriptions/{subscriptionId} +``` +PUT /webrtc-events/v0.2/subscriptions/sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890 HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: f8e7d6c5-b4a3-2190-fedc-ba0987654321 + +{ + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.xyz789", + "accessTokenExpiresUtc": "2026-01-20T23:59:59.999Z", + "accessTokenType": "bearer" + }, + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2026-01-31T23:59:59.999Z" + } +} +``` +> **ISSUE** (NotAddressed) +> +> Related Issue: #78 +> +> Related PR: #NN +> +> When a `session-status` event subscription expires, signaling for ongoing calls becomes unavailable. Since media modifications may be initiated by the Remote Endpoint, clients MUST refresh the subscription using PUT before `expiresAt` or `sinkCredential.accessTokenExpiresUtc` is reached, if they have ongoing media sessions. +> +> The `PUT` method for subscription refresh must be added to the webrtc-events.yaml. + +#### [21] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: f8e7d6c5-b4a3-2190-fedc-ba0987654321 + +{ + "protocol": "HTTP", + "sink": "https://asp.example.com/webhooks/webrtc", + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2026-01-31T23:59:59.999Z" + }, + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "startsAt": "2025-12-15T10:30:00.000Z", + "expiresAt": "2026-01-31T23:59:59.999Z", + "status": "ACTIVE" +} +``` + +## 3.1.3. Unsubscribe from events +### 3.1.3.1. Sequence + +![fig3](./subscription_for_webrtc_events_fig-3.png) + +### 3.1.3.2. Example messages +#### [29] DELETE /webrtc-events/{apiVersion}/subscriptions/{subscriptionId} +``` +DELETE /webrtc-events/v0.2/subscriptions/sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890 HTTP/1.1 +Host: api.example.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 +``` + +#### [32] 202 Accepted +``` +HTTP/1.1 202 Accepted +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890" +} +``` + +#### [33] POST {sink} (callback) +``` +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.xyz789 +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "id": "evt-9a8b7c6d-5e4f-3210-fedc-ba9876543210", + "source": "https://api.example.com/webrtc-events/v0.2", + "type": "org.camaraproject.webrtc-events.v0.subscription-ended", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-12-15T14:30:00.000Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "terminationReason": "SUBSCRIPTION_DELETED", + "terminationDescription": "Subscription deleted by client request" + } +} +``` + +#### [35] 204 No Content (callback response) +``` +HTTP/1.1 204 No Content +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +``` diff --git a/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration/raw.md b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..4974bce8d705c71ecce59e54bab6db330b797d65 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration/raw.md @@ -0,0 +1,150 @@ +# 3.2. WebRTC Registration + +This part of the call flow covers WebRTC registration. + +## 3.2.1. WebRTC Registrations +### 3.2.1.1. Sequence + +![fig1](./webrtc_registration_fig1.png) + +### 3.2.1.2. Example messages + +#### [6] POST /webrtc-registration/{apiVersion}/sessions +``` +POST /webrtc-registration/v0.3/sessions HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2", + "registrationExpireTime": "2025-12-31T23:59:59.999Z" +} +``` + +> **NOTE** +> +> Depending on the WebRTC registration, SIP REGISTER may either be omitted or performed: +> +> - When the Telco network assigns specific phone number ranges to the WebRTC Gateway and accepts SIP INVITE for call routing, SIP REGISTER is omitted. +> - When a SIP account is issued for each phone number used for interworking from WebRTC, SIP REGISTER is performed. +> +> Even when SIP REGISTER is performed, it should be noted that the WebRTC Gateway does not have a SIM and therefore cannot use AKA′ authentication, making it different from IMS UE Registration. + + + + +#### [9] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "registrationId": "reg-12345678-abcd-ef90-1234-567890abcdef", + "regInfo": { + "phoneNumber": "+123456789", + "regStatus": "Registered" + }, + "expiresAt": "2025-12-31T23:59:59.999Z" +} +``` + +> **NOTE** +> +> The API Provider may define minimum, maximum, and default values for the WebRTC registration validity period. If the requested duration ("registrationExpireTime" - currentTime) is within the acceptable range, 'expiredAt' may be set to the requested value. +> +> Otherwise, the API Provider may either use (currentTime + default value) for 'expiredAt' or return an error. + + +## 3.2.2. Refresh WebRTC Registrations +### 3.2.2.1. Sequence + +![fig2](./webrtc_registration_fig2.png) + +### 3.2.2.2. Example messages + +#### [15] PUT /webrtc-registration/{apiVersion}/sessions/{registrationId} +``` +PUT /webrtc-registration/v0.3/sessions/reg-12345678-abcd-ef90-1234-567890abcdef HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "registrationExpireTime": "2026-01-15T12:00:00.000Z" +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #144 +> +> Related PR: #NN +> +> The description of the expiration time after update in the PUT operation only considers the case where the API Consumer does not specify a desired expiration time in the PUT request. The description needs to be revised. +> +> Informational descriptions for above need to be revised in webrtc-registration.yaml. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #145 +> +> Related PR: #NN +> +> PUT (update) should be used by the API Consumer to request refreshing existing WebRTC registrations before expiration based on monitoring expiredAt, while POST (new registration) should be used after receiving registration-ends. +> +> Informational descriptions for above need to be added in webrtc-registration.yaml for clarification. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #146 +> +> Related PR: #NN +> +> When registration expires, initiating new calls (both incoming and outgoing) is no longer possible. The following behaviors need clarification: +> - Should ongoing media sessions be disconnected? +> - Should any remaining WebRTC event subscription resources associated with the related deviceId be deleted? +> +> If these behaviors are not implementation-dependent, they should be documented as informational descriptions in the webrtc-registration.yaml or webrtc-events.yaml to clarify the expected behavior. + +#### [18] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "regInfo": { + "phoneNumber": "+123456789", + "regStatus": "Registered" + }, + "registrationId": "reg-12345678-abcd-ef90-1234-567890abcdef", + "expiresAt": "2026-01-15T12:00:00.000Z" +} +``` + +## 3.2.3. WebRTC De-Registrations +### 3.2.3.1. Sequence + +![fig3](./webrtc_registration_fig3.png) + +### 3.2.3.2. Example messages + +#### [24] DELETE /webrtc-registration/{apiVersion}/sessions/{registrationId} +``` +DELETE /webrtc-registration/v0.3/sessions/reg-12345678-abcd-ef90-1234-567890abcdef HTTP/1.1 +Host: api.example.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: c3d4e5f6-a7b8-9012-cdef-345678901234 +``` + +#### [27] 204 No Content +``` +HTTP/1.1 204 No Content +x-correlator: c3d4e5f6-a7b8-9012-cdef-345678901234 +``` + + diff --git a/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams/README/raw.md b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..416fb09b59265e3703856abcdada2207642b1214 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/uml-diagrams/README/raw.md @@ -0,0 +1,26 @@ +# UML diagrams + +This folder includes UML files and PNG rederizations of the three main use cases. + +- [UML diagrams](#uml-diagrams) + - [WebRTC Events sucription](#webrtc-events-sucription) + - [WebRTC Registration process](#webrtc-registration-process) + - [WebRTC Call handling](#webrtc-call-handling) + - [Originating use case (create a call)](#originating-use-case-create-a-call) + - [Terminating use case (receive a call)](#terminating-use-case-receive-a-call) + +## WebRTC Events sucription + +![WebRTC EventsSubscription]() + +## WebRTC Registration process + +![WebRTC Registration]() + +## WebRTC Call handling + +### Originating use case (create a call) +![WebRTC CallHandling ORIG]() + +### Terminating use case (receive a call) +![WebRTC CallHandling TERM]() \ No newline at end of file diff --git a/marked/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering/raw.md b/marked/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..ec04487a100f6fa1ea66e48684ec5075899db21c --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering/raw.md @@ -0,0 +1,101 @@ +# Obtaining a WebRTC SDP to create calls + +CAMARA `webrtc-call-handling` API requires basic usage of the WebRTC API to create +calls. To put it simply, you need to obtain and create an `SDP`(Session Description +Protocol) body to use in the call creation. + +Let's dig on it on this document. + +Browsers offer the [WebRTC API](https://developer.mozilla.org/en-US/docs/Web/API/WebRTC_API) +that include `getUserMedia()` to obtain access to media devices (microphone and +cameras), and `RTCPeerConnection` interface to create a network connection and +deliver the captured media to a far end. + +That technology becomes responsible of most our common real-time communications on +the web nowadays, from broadcasting to video conference solutions. + +The `RTCPeerConnection` interface, provides an `SDP`that is required by our CAMARA +webrtc-call-handling API. So we are going to explain how to obtain it. + +Here is a simple code that you can test on your browser: + +``` +async function getAudioSDP() { + const config = { iceServers: [{ urls: "stun:stun.l.google.com:19302" }] }; + const peerConnection = new RTCPeerConnection(config); + + try { + // Get the audio stream + const stream = await navigator.mediaDevices.getUserMedia({ audio: true }); + stream.getTracks().forEach(track => peerConnection.addTrack(track, stream)); + + // Create an offer and set it as local description + const offer = await peerConnection.createOffer(); + await peerConnection.setLocalDescription(offer); + + // Collect ICE candidates + const candidates = []; + peerConnection.onicecandidate = (event) => { + if (event.candidate) { + candidates.push(event.candidate); + } else { + // No more candidates, log the result + const sdpData = { + sdp: peerConnection.localDescription.sdp, + candidates: candidates.map(c => c.candidate) + }; + console.log("SDP body:", JSON.stringify(sdpData, null, 2)); + } + }; + } catch (error) { + console.error("Error accessing microphone:", error); + } +} + +// Run the function +getAudioSDP(); +``` + +Maybe it will take a while to resolve the promise, but once you get it, you will +have a valid description for your session using the `SDP`standard +protocol. + +Here is an example of received SDP. You can safely ignore the `candidates` field +and use only the `sdp` value: + +``` +SDP body: { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n", + "candidates": [ + "candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 ufrag YoUo network-cost 999", + "candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 ufrag YoUo network-cost 999" + ] +} +``` + +Since there is a delay between the request and the creation of the peer connection +we can start the call creation using POST, and update the session using PUT and +including the new `SDP`and newer candidates obtained. + +## Using the SDP to create calls + +Here an example of **call creation** using the CAMARA webrtc-call-handling API +with the local `SDP` description gathered on the previous example: + +``` +POST /webrtc-call-handling/v0.2/sessions +{ + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + "offer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + }, + "clientCorrelator": "fda6e26d-e7c8-4596-870c-c083c0d39b2c" +} +``` + +Check extra information about this API on the inline YAML documentation or refer +to other supporting documents within this folder. + +Happy webrtc-ing! + diff --git a/marked/WebRTC/documentation/SupportingDocuments/webrtc_voice_api/raw.md b/marked/WebRTC/documentation/SupportingDocuments/webrtc_voice_api/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e448b46c809a2521fabed1f7447b931fa983b5d0 --- /dev/null +++ b/marked/WebRTC/documentation/SupportingDocuments/webrtc_voice_api/raw.md @@ -0,0 +1,129 @@ +# Overview + +Bring your own number (BYON) service aims to provide consumers with the ability to use their phone number (MSISDN) for outgoing and incoming calls from non-SIM card devices. To access the service, users are required to authenticate using their digital credentials associated with their MNO account, in example their operator app credentials. As registration from a web endpoint is necessary to enable the service on non-SIM card devices. + +Outgoing calls made through the service will display the user's MSISDN as the caller number, ensuring that the recipient recognizes the user's phone number on their caller ID. + +Incoming calls introduce a unique functionality whereby multiple devices will ring simultaneously. This includes the user's smartphone and the web endpoint they have registered from. This design enables users to conveniently answer calls from any of these devices, depending on their preference or accessibility. The service is compatible with various devices that support web browsing environments, such as laptops, PCs, and XR immersive glasses. + +The service specification emphasises the accessibility and flexibility of utilising one's phone number across different non-SIM card devices. By leveraging this web-based service, users can extend their communication capabilities beyond traditional SIM-based devices, enhancing their overall communication experience. + +## Introduction + +This service brings new functionalities for the WebRTC services whose idea is to integrate BYON API to maintain the client number in out-bound and in-bound calls from web comms service. + +**Out-bound calls:** + +- Recipient receives call as if it was from User's normal phone number. +- Maintains common number through web communication service and standard subscription. +- Facilitates number recognition and call-back for co-workers, partners and/or clients. + +**In-bound calls:** + +- Receive phone calls simultaneously on phone subscription and web communication service. +- Presents 'Occupied user' info to caller user is already in phone call. +- Facilitates common multi-channel contact with co-workers, partners and/or clients. + +## API Spec + +### Roles, Actors and Scope + +Roles: Customer-user + +Actors: Application service providers, hyperscalers, application developers. + +Scope: + +1. Register to Network – Register the client endpoint instance to MNO's IMS Network. +2. Create Notification Channel – Create Notification channel of specified type to receive notifications from the network (e.g. incoming call). +3. Place an Out Call – Place an outbound voice call request to the MNO's IMS Network. +4. Receive an Incoming Call - Receive an incoming call request from the MNO's IMS network. + +### Authentication and Authorization + +The defined APIs uses OAUTH 2.0 client credentials and uses the Access Token granted by the CSP's IDP for its usage. This must be the initial procedure to be completed before invoking any of the service APIs. + +### Pre-Conditions + +The preconditions are listed below: + +- The customer-user must have operator/MNO (provider of the native MSISDN) provided credentials to login to the web app. + +### Activities/Steps + +- Starts when: The customer-user logs into the communication application in the browser. +- Ends when: The customer-user logs out of the communication application in the browser or closes the browser. + +### Post-Conditions + +The customer-user places an outgoing voice call or accepts an incoming voice call. + +### Exceptions + +Several exceptions might occur during the API operations, + +- Unauthorized: Invalid credentials. +- \ + +### API Endpoint details + +**Registration and Connection Management (RACM)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /session | Create a RACM session | Registers the client instance into MNO's IMS Network via the WebRTC Gateway. This request will include the Access Token received from the MNO's IDP (auth server).On successful RACM session creation, the client endpoint reusing the device's MSISDN will be successfully registered in MNO's IMS network, ready to accept any call origination or termination request. | +| PUT /session/{sessionId} | Modify a RACM session | This modification request is to share refreshed Access Token received from MNO's IDP (auth server). | +| DELETE /session/{sessionId} | Delete a RACM session | When the customer-user gracefully logs out of the application, the RACM session will be deleted, resulting in de-registration from the MNO's IMS network. | + +**Notification Channel Management** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /channels | Create a Notification channel | Creates a notification channel of specified type (e.g. Websocket, PNS, webhook) in order to receive notifications from the network. These notification channels will be used to send following notifications from the network, +- Incoming call (network -\> client) +- Any other notifications from the network such as call setup status, call modification status, etc. + | + +**OneToOne Call (outgoing)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /session | Create a Voice session | Create an Outbound (1-1) Voice session. This request when received at the WebRTC GW triggers an outgoing call request into the MNO's IMS network. The call setup status (inprogress, ringing, connected, release) is sent over the websocket notification channel. | +| PUT /session/{sessionId}/status | Modify a Voice session | This modification request is to modify the call object attributes such as media properties included in the SDP (e.g. call placed on hold). | +| DELETE /session/{sessionId} | Delete a Voice session | When the call is released from the client's end, the corresponding Voice session object is deleted, which will trigger the WebRTC GW to initiate a Call release into the CSP's IMS network. | +| | | When the call is released from the network's end, the call release notification is sent over the websocket notification channel, which will result in deleting of the Voice session object. | + +**OneToOne Call (incoming)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| | | Notification for inbound call is received via the websocket notification channel. The Voice session object is created by default prior to sending this inbound call notification. | +| PUT /session/{sessionId}/status | Modify a Voice session | This modification request is to modify the call object attributes such as media properties included in the SDP (e.g. call placed on hold). | +| DELETE /session/{sessionId} | Delete a Voice session | When the call is terminated from the client's end, the corresponding Voice session object is deleted, which will trigger the WebRTC GW to initiate a Call release into the MNO's IMS network. | +| | | When the call is released from the network's end, the call release notification is sent over the websocket notification channel, which will result in deleting of the Voice session object. | + +### Event status enumeration + +There are defined a series of status for the call. These status are used by the session endpoint for PUT actions and also used by the event notification channel. + +Status are: + +| Status | SIP Response | Description | +| ------ | ------------ | ----------- | +`Initial` | n/a | Initial status of transaction +`InProgress` | 183 Session progress | Updated info about a session +`Ringing` | 180 Ringing | Destination user agent is alerting the user +`Proceding` | n/a | Call progressing +`Connected` | 200 OK | Session in place +`Terminated` | n/a | The call is being terminated, but not defined the reason. It needs to add a "reason" +`Hold` | n/a | Status when a call on hold +`Resume` | n/a | Status for a call that is resumed +`SessionCancelled` | n/a | 487 Resquest terminated or CANCEL+200OK +`Declined` | 603 Decline | The destination does not want to participate +`Failed` | 412 / 430 | Call terminated and failed without 200 OK +`Waiting` | 182 Queued | Call pending to be processed +`NoAnswer` | 408 Request Timeout | No answer before timer expires +`NotReachable` | 404 Not found | Destination requested not found +`Busy` | 486 Busy here | Callee is busy + +Ref. for status mapping: https://www.gsma.com/newsroom/wp-content/uploads//NG.114-v1.0-3.pdf \ No newline at end of file diff --git a/marked/eSimRemoteManagement/README/raw.md b/marked/eSimRemoteManagement/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..f72f7e7a10e6b7439697b0a1735cbf53b7042726 --- /dev/null +++ b/marked/eSimRemoteManagement/README/raw.md @@ -0,0 +1,42 @@ + + + + + + + + + +# eSimRemoteManagement + +Sandbox API Repository to describe, develop, document, and test the eSimRemoteManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/K4CbFg) + +## Scope + +* Service API(s) “eSimRemoteManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Provide eSIM-based remote management capability, allowing users to remotely manage the status of profiles on the device's eUICC and complete remote operations such as downloading, activating, de-activating or deleting. +* Describe, develop, document, and test the API(s) +* Started: December 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + * Schedule: Weekly on Thursday 16:00 CST / 10:00 CEST + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96461951353?password=150ba7bb-550f-40f6-b8b2-82e67d36ac4e) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/eSIMRemoteManagement) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . \ No newline at end of file diff --git a/marked/eSimRemoteManagement/code/API_definitions/README/raw.md b/marked/eSimRemoteManagement/code/API_definitions/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..e9cd5a56c4c09578a451293b7a3a128b8bb4fc65 --- /dev/null +++ b/marked/eSimRemoteManagement/code/API_definitions/README/raw.md @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/marked/eSimRemoteManagement/code/API_definitions/esim-remote-management/raw.md b/marked/eSimRemoteManagement/code/API_definitions/esim-remote-management/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..c250660990e5d0d6aa762a1368ea056f0482cb35 --- /dev/null +++ b/marked/eSimRemoteManagement/code/API_definitions/esim-remote-management/raw.md @@ -0,0 +1,858 @@ +# esim-remote-management + +```yaml +--- +openapi: 3.0.3 +info: + title: eSIM Remote Management + description: > + Provide eSIM-based remote management capability, allowing users to remotely manage the status of profiles on the device's eUICC and complete remote operations such as downloading, activating, de-activating or deleting. + + # Introduction + + The eIM Platform API provides a comprehensive, secure, and standardized interface for device manufacturers (OEMs) and ecosystem partners to remotely manage eSIM profiles on connected devices. This API empowers you to offer seamless connectivity lifecycle management directly within your device ecosystem. + + # API Functionality + + The API provides the following functionality: + - Profile Download & Installation: Securely provision and download new eSIM profiles to devices, based on user subscription, geographic location, or specific business triggers. + - Profile Inventory Query: Retrieve a detailed list of all eSIM profiles currently stored on a device, including their status (e.g., enabled, disabled, pending download), associated ICCID/EID, and service provider information. + - Profile Lifecycle Management: Execute precise control over installed profiles: + - Activation/Enable: Switch a downloaded profile to the active state for live connectivity. + - Deactivation/Disable: Temporarily disable a profile without deleting it from the device. + - Deletion: Permanently remove an unused or obsolete profile from the device's eSIM chip, freeing up memory. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/ ) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/eSimRemoteManagement +servers: + - url: "{apiRoot}/eSimRemoteManagement/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: eSIMRemoteManagement + description: API operation to eSIM Remote Management +paths: + /profile/list-syn: + post: + security: + - openId: + - esim-remote-management:listSyn + tags: + - eSIMRemoteManagement + operationId: profileListSyn + summary: Profile List Synchronization + description: Synchronize Profile list + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + /profile/status/enquiry: + post: + security: + - openId: + - esim-remote-management:enquiry + tags: + - eSIMRemoteManagement + operationId: profileStatusEnquiry + summary: Profile Status Enquiry + description: Query Profile status + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + timestamp: + type: string + description: Request timestamp + sequenceNum: + type: string + description: Sequence number + clientId: + type: string + description: Client ID + data: + type: object + properties: + iccid: + type: string + description: ICCID + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + data: + type: object + properties: + eId: + type: string + description: EID + isUsed: + type: integer + description: Profile usage status 0 Not used, 1 Used + default: 0 + maxUsedCount: + type: integer + description: Maximum download count for Profile + default: 1 + usedCount: + type: integer + description: Usage count of Profile + default: 0 + modifyTime: + type: string + description: Modification time + /profile/set/fallback/attribute: + post: + security: + - openId: + - esim-remote-management:attribute + tags: + - eSIMRemoteManagement + operationId: profileSetFallbackAttribute + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + timestamp: + type: string + description: Request timestamp + sequenceNum: + type: string + description: Sequence number + clientId: + type: string + description: Client ID + data: + type: object + properties: + eId: + type: string + description: EID + imei: + type: string + description: Device ID + iccid: + type: string + description: ICCID to operate on + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + data: + type: object + properties: + taskId: + type: string + description: Task ID + /profile/result/query: + post: + security: + - openId: + - esim-remote-management:query + tags: + - eSIMRemoteManagement + operationId: profileResultQuery + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileResultQueryReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileResultQueryResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/oper: + post: + security: + - openId: + - esim-remote-management:oper + tags: + - eSIMRemoteManagement + operationId: profileOperation + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileOperReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileOperResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/downloaded-list: + post: + security: + - openId: + - esim-remote-management:downloadedlist + tags: + - eSIMRemoteManagement + operationId: profileList + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqEIdProfileListReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespEIdProfileListResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/download: + post: + security: + - openId: + - esim-remote-management:download + tags: + - eSIMRemoteManagement + operationId: profileDownload + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileDownloadReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileDownloadResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /eid-status-enquiry: + post: + security: + - openId: + - esim-remote-management:enquiry + tags: + - eSIMRemoteManagement + operationId: eIdStatusEnquiry + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqEIdStatusEnquiryReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespEIdStatusEnquiryResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + type: openIdConnect + description: to support Consent Management + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + schemas: + BaseCmpReqProfileResultQueryReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + description: Client ID + data: + $ref: '#/components/schemas/ProfileResultQueryReq' + ProfileResultQueryReq: + type: object + properties: + taskId: + type: string + BaseCmpRespProfileResultQueryResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/ProfileResultQueryResp' + ProfileResultQueryResp: + type: object + properties: + taskId: + type: string + imei: + type: string + iccid: + type: string + operResult: + type: integer + description: 'Operation profile result: + - 0: executing. + - 1: Operation success. + - 2: Operation fail.' + enum: [0, 1, 2] + eId: + type: string + resultMsg: + type: string + description: Result message + BaseCmpReqProfileOperReq: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + $ref: '#/components/schemas/ProfileOperReq' + ProfileOperReq: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + optType: + type: integer + description: Operation type 1 Enable, 2 Disable, 3 Delete + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpRespProfileOperResp: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + $ref: '#/components/schemas/ProfileOperResp' + ProfileOperResp: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + optType: + type: integer + description: Operation type 1 Enable, 2 Disable, 3 Delete + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpReqEIdProfileListReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + description: Client ID + data: + $ref: '#/components/schemas/EIdProfileListReq' + EIdProfileListReq: + type: object + properties: + eId: + type: string + BaseCmpRespEIdProfileListResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/EIdProfileListResp' + EIdProfileListResp: + type: object + properties: + imei: + type: string + profiles: + type: array + items: + $ref: '#/components/schemas/ProfileInfo' + eId: + type: string + ProfileInfo: + type: object + properties: + iccid: + type: string + enableStatus: + type: integer + format: int32 + BaseCmpReqProfileDownloadReq: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + $ref: '#/components/schemas/ProfileDownloadReq' + ProfileDownloadReq: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + autoEnableType: + type: integer + description: Download and activate option 1 Download and enable + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpRespProfileDownloadResp: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + $ref: '#/components/schemas/ProfileDownloadResp' + ProfileDownloadResp: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + autoEnableType: + type: integer + description: Download and activate option 1 Download and enable + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpReqEIdStatusEnquiryReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + data: + $ref: '#/components/schemas/EIdStatusEnquiryReq' + EIdStatusEnquiryReq: + type: object + properties: + eId: + type: string + BaseCmpRespEIdStatusEnquiryResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/EIdStatusEnquiryResp' + EIdStatusEnquiryResp: + type: object + properties: + enableIccid: + type: string + imei: + type: string + syncTime: + type: string + eId: + type: string + ErrorInfo: + type: object + required: + - status + - code + - detail + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + detail: + type: string + description: Detailed error description + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + detail: Client specified an invalid argument, request body or query param + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + detail: Request not authenticated due to missing, invalid, or expired credentials + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + detail: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + detail: Phone number cannot be deducted from access token context + Generic404: + description: Resource Not Found + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + detail: A specified resource is not found + Generic500: + description: Server error + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + detail: Server error + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + detail: Service unavailable +``` diff --git a/marked/eSimRemoteManagement/documentation/API_documentation/README/raw.md b/marked/eSimRemoteManagement/documentation/API_documentation/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/eSimRemoteManagement/documentation/API_documentation/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/marked/eSimRemoteManagement/documentation/SupportingDocuments/README/raw.md b/marked/eSimRemoteManagement/documentation/SupportingDocuments/README/raw.md new file mode 100644 index 0000000000000000000000000000000000000000..37aa0ff405bf918d942905c10a0f435fd46c8ffd --- /dev/null +++ b/marked/eSimRemoteManagement/documentation/SupportingDocuments/README/raw.md @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationEndpointDiscovery/README.md b/original/ApplicationEndpointDiscovery/README.md new file mode 100644 index 0000000000000000000000000000000000000000..e37252cb68cdac08df9e55de502d81327e740f69 --- /dev/null +++ b/original/ApplicationEndpointDiscovery/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationEndpointDiscovery + +Sandbox API Repository to describe, develop, document, and test the ApplicationEndpointDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAtC) + +## Scope + +* Service API(s) “ApplicationEndpointDiscovery” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Discover the optimal application endpoint(s) that a given end-user's device can connect to. +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationEndpointDiscovery/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-endpoint-discovery v0.1.0** + [[YAML]](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/r1.2/code/API_definitions/application-endpoint-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointDiscovery/r1.2/code/API_definitions/application-endpoint-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointDiscovery/r1.2/code/API_definitions/application-endpoint-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationEndpointDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationEndpointDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery.yaml b/original/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery.yaml new file mode 100644 index 0000000000000000000000000000000000000000..ed433d97741376b9d9b6a5b9ec19472f112d1fb5 --- /dev/null +++ b/original/ApplicationEndpointDiscovery/code/API_definitions/application-endpoint-discovery.yaml @@ -0,0 +1,908 @@ +--- +openapi: 3.0.3 +info: + title: Application Endpoint Discovery + version: wip + description: | + The Application Endpoint Discovery API returns the optimal application + endpoint(s) that a given end-user's device can connect to. + + # Introduction + + Operators often host multiple Edge Cloud Zones across various territories. + Connecting an application directly to the optimal application instance + endpoint in an Edge Cloud Zone may minimize latency. + + The Application Endpoint Discovery API extends beyond the capabilities of + the Simple Edge Discovery API by not only locating the optimal + Edge Cloud Zone but also providing the direct link to the specified + application's endpoint within that Edge Cloud Zone. This approach ensures + that developers can instantly integrate this endpoint into their + applications, improving user experience. + + After identifying the optimal application endpoint(s) through the API, + API consumers can: + * Connect their application client directly to the chosen application + endpoint(s), enhancing the responsiveness of the service. + * If no suitable endpoints are available, the developer can use other APIs + to instantiate new instance and/or register new application endpoints. + + The optimal endpoint(s) are calculated by the Edge Cloud Provider based on + the following factor: shortest network path to the network-attached + device identified in the API request. Future releases of this API might + add other factors to obtain them. + + # Relevant terms and definitions + + - `Application Profile:` A profile which represents an application's + networking demands (latency, jitter, bandwidth rates). + - `Application Provider:` The provider of the application that is deployed + on the Edge Cloud. + - `Application Endpoint:` An application server IP address or FQDN, and + port exposed by an application instance to allow connections from clients. + - `Application Instance:` An instantiation of an Application running on + an Edge Cloud Zone. It is assumed that for each application, a maximum of + one logical instance can run per Edge Cloud Zone. + - `Device:` End-user equipment able to connect to a mobile network (i.e. + smartphone, IoT sensor/actuator). + - `Edge Cloud Zone:` Availability Zone in an Edge Cloud. It is the lowest + level of abstraction exposed to an Application Provider who wants to + deploy an Application on Edge Cloud. Availability Zones exist within + a Region. + + # API Functionality + + The API can be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet), or by a server. + + There is a single API service endpoint: + + - `POST /retrieve-optimal-app-endpoints` + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `device:` End-user equipment able to connect to a mobile network. The + developer can choose to provide the below specified device identifiers: + - `ipv4Address:` Public IP address (IPv4) of the user device, which can be + fetched via external IP discovery services. + - `ipv6Address:` Public IP address (IPv6) of the user device, which can be + fetched via external IP discovery services. + - `phoneNumber:` The device's phone number in international E.164 format. + - `networkAccessIdentifier:` A unique identifier provided by the network + operator (where supported). + - One of the following application identifiers: + - `appId:` A unique identifier for an application onboarded on the Edge + Cloud. It is used when the application has been onboarded using the Edge + Application Management API. + - `applicationEndpointsId:` A unique identifier for the registered + application endpoint(s). It is used when the application has not been onboarded + using the Edge Application Management API, and available endpoints have been + registered by the Edge Application Registration API. Every endpoint registered + under the same `applicationEndpointsId` identifier belongs to the same + application. + + ## Outputs + + If successful, a `200 OK ` response code is returned with a JSON object + containing the following data: + + - `applicationEndpoints:` An array containing at least one Application Endpoint + object. Each Application Endpoint object includes the following parameters: + - `port:` TCP or UDP port number exposed by the application instance. + - One of the following parameters which define the endpoint: + - `ipv4addresses:` Array of IPv4 addresses exposed by the application + instance. + - `ipv6addresses:` Array of IPv6 addresses exposed by the application + instance. + - `fqdn:` Fully Qualified Domain Name exposed by the application instance. + - `applicationEndpointDescription:` Optionally, a string that describes the + application endpoint. + - `edgeCloudZone:` Optionally, object that identifies the Edge Cloud Zone + the application endpoint belongs to, including: `edgeCloudZoneId`, + `edgeCloudZoneName`, `edgeCloudZoneStatus`, `edgeCloudRegion`, and + `edgeCloudProvider`. + - One of the following application identifiers (the one provided on the request) + - `appId:` A unique identifier for an application onboarded on the Edge + Cloud. It is used when the application has been onboarded using the Edge + Application Management API. + - `applicationEndpointsId:` A unique identifier for the registered + application endpoint(s). It is used when the application has not been onboarded + using the Edge Application Management API, and available endpoints have been + registered by the Edge Application Registration API. Every endpoint + registered under the same `applicationEndpointsId` identifier belongs to + the same application. + - `applicationServerProviderName:` Optionally, the Application Provider + identifier + - `applicationProfileId:` Optionally, the Application Profile identifier + - `device`: End-user equipment identifier used to obtain the optimal application + endpoint. It is only included when multiple device identifiers come in the + request. + - The `Device` object allows the API consumer to provide more than one device + identifier. No error will be returned when the supplied device identifiers + do not match with the same device. It is responsibility of the API consumer + to ensure that the identifiers they are using are associated with the same + device. + - Where an API consumer provides more than one device identifier, the + response will indicate which of these identifiers have been used to fulfil + the API, even if the identifiers do not match the same device. The + `DeviceResponse` object is defined for this purpose. + + + ## Errors + + - If the API call contains a formatting or other any other syntatic error, + a `400 INVALID_ARGUMENT` error is returned. + - If the API call cannot be authenticated due to missing, invalid, or + expired credentials, a `401 UNAUTHENTICATED` error is returned. + - If the API call has a valid access token that does not have the + required scope, then a `403 PERMISSION_DENIED` error is returned. + - If the API call has a valid access token that does not identify + a single device, then a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API call has an `appId` that does not identify a valid + application on the Edge Cloud, a `404 NOT_FOUND` error is returned. + - If the API call has an `applicationEndpointsId` that does not identify + any registered endpoint on the Edge Cloud, a `404 NOT_FOUND` error + is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will + be identified from the optional `device` object, which therefore MUST be + provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged + access token to invoke the API by relying on the information that is + associated with the access token and was identified during the + authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `device` object is not included in the request, then the server + will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional + `device` object is also included in the request, then the server will + return an error with the `422 UNNECESSARY_IDENTIFIER` error code. + This will be the case even if the same device is identified by + these two methods, as the server is unable to make this comparison. + - If the subject cannot be identified from the access token and the + optional `device` object only includes device identifiers not supported + by the implementation, then the server will return an error with the + `422 UNSUPPORTED_IDENTIFIER` error code. + - If the service is not applicable for the subject that is identified + from the access token or the optional `device` object, then the server + will return an error code with the `422 SERVICE_NOT_APPLICABLE` error + code. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + --- + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ApplicationEndpointDiscovery +servers: + - url: "{apiRoot}/application-endpoint-discovery/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by the service provider, e.g. `api.example.com` or + `api.example.com/somepath` + +tags: + - name: Application Endpoint Discovery + description: | + Find the optimal Application Instance Endpoint(s) to the user device. +paths: + /retrieve-optimal-app-endpoints: + post: + security: + - openId: + - application-endpoint-discovery:app-endpoints:read + operationId: getOptimalAppEndpoints + parameters: + - name: x-correlator + in: header + required: false + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/EndpointDiscoveryInfo" + examples: + Identify Device By 3-Legged Access Token and AppId: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedTokenAppId' + Identify Device By Phone Number and AppId: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumberAppId' + Identify Device By IP Address and ApplicationEndpointsId: + $ref: '#/components/examples/IdentifyDeviceByIPAddressAppEndpointsId' + Identify Device By Multiple Identifiers and AppId: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiersAppId' + responses: + "200": + description: | + Successful response, returning the optimal Application Instance + Endpoint(s) to the user device identified in the request body. + The response will include the endpoint(s) exposed by the Application + Instance(s) with the shortest network path to the end user device + identified in the request. There can be multiple application endpoints + returned in the response and the API consumer can choose the one that best + suits their needs. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/EndpointDiscoveryResult" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Application Endpoint Discovery + summary: | + Returns the Endpoint(s) of the optimal Application Instance(s) to the user + device identified in the request. + description: | + On receiving this request, the network will return the endpoint(s) + of the Application Instance(s) with the shortest network path to the + end user device identified in the request. +components: + securitySchemes: + openId: + description: OpenID Provider Configuration Information. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified + device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these + options. The API invoker can provide multiple identifiers to be + compatible across different network operators. In this case the + identifiers MUST belong to the same device. + + NOTE2: as for this Commonalities release, we are enforcing that + the networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/SingleIpv6Addr" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the + network that the response refers to. This parameter is only + returned when the API consumer includes the `device` parameter in + their request (i.e. they are using a two-legged access token), and + is relevant when more than one device identifier is specified, as + only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in + their request, the API provider must return a single identifier + which is the one they are using to fulfil the request, even if the + identifiers do not match the same device. API provider does not + perform any logic to validate/correlate that the indicated device + identifiers match the same device. No error should be returned if + the identifiers are otherwise valid to prevent API consumers + correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has + to be formatted in international format, according to E.164 + standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. + In 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least + one of either privateAddress or publicPort, dependent upon which is + known. In general, mobile devices cannot be identified by their + public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + SingleIpv6Addr: + description: | + The device should be identified by the observed IPv6 address, or by + any single IPv6 address from within the subnet allocated to the + device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + EndpointDiscoveryInfo: + description: | + Element to retrieve the optimal application endpoint(s) for the + identified device. + type: object + anyOf: + - required: [applicationEndpointsId] + - required: [appId] + properties: + device: + $ref: "#/components/schemas/Device" + applicationEndpointsId: + $ref: "#/components/schemas/ApplicationEndpointsId" + appId: + $ref: "#/components/schemas/AppId" + + ApplicationEndpointsId: + description: | + A system-defined string identifier representing + one or more registered Application Endpoints that belong + to the same application. + type: string + format: uuid + example: "4d596ac1-7822-4927-a3c5-d72e1f922c94" + + AppId: + type: string + format: uuid + description: | + A globally unique identifier associated with the application. + This GUID will have been previously provided by the Edge Cloud Zone + provider. + example: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + EndpointDiscoveryResult: + description: | + Endpoint Discovery result including optimal application endpoint(s) + for the requested identified device. + type: object + required: + - applicationEndpoints + anyOf: + - required: [applicationEndpointsId] + - required: [appId] + properties: + applicationEndpoints: + description: Array of Application Endpoints. + type: array + items: + $ref: "#/components/schemas/ApplicationEndpoint" + minItems: 1 + appId: + $ref: "#/components/schemas/AppId" + applicationEndpointsId: + $ref: "#/components/schemas/ApplicationEndpointsId" + applicationServerProviderName: + type: string + description: Unique ID representing the Edge Application Provider + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/DeviceResponse" + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + + EdgeCloudZoneId: + description: A unique identifier for the Edge Cloud Zone. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + EdgeCloudRegion: + description: | + The EdgeCloudProvider's name for the region where the Edge Cloud + Zone is located. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + EdgeCloudProvider: + description: The provider of the Edge Cloud. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ProviderA" + + EdgeCloudZoneName: + description: The name of the Edge Cloud Zone. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ZoneA" + + ApplicationProfileId: + description: A unique identifier for the application profile. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + ApplicationEndpoint: + type: object + description: | + An application server IP address or FQDN with a port, + exposed by an application instance deployed on the Edge Cloud + provider. + required: + - port + anyOf: + - required: [fqdn] + - required: [ipv4Addresses] + - required: [ipv6Addresses] + properties: + fqdn: + $ref: "#/components/schemas/Fqdn" + ipv4Addresses: + description: Array of IPv4 addresses. + type: array + items: + $ref: "#/components/schemas/Ipv4Address" + minItems: 1 + ipv6Addresses: + description: Array of IPv6 addresses. + type: array + items: + $ref: "#/components/schemas/Ipv6Address" + minItems: 1 + port: + $ref: "#/components/schemas/Port" + edgeCloudZone: + $ref: "#/components/schemas/EdgeCloudZone" + applicationEndpointDescription: + type: string + description: Description of the application endpoint + + Fqdn: + type: string + description: Fully Qualified Domain Name. + + Ipv4Address: + type: string + description: | + A single IPv4 address specified in dotted-quad form like 1.2.3.4. + example: "198.51.100.1" + + Ipv6Address: + type: string + description: | + A single IPv6 address, following IETF 5952 format like + 2001:db8:85a3:8d3:1319:8a2e:370:7344. + example: "2001:db8:85a3::8a2e:370:7334" + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: | + Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter criteria + combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: | + Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: | + Permission denied. OAuth2 token access does not have the + required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: | + Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: | + An identifier is not included in the request and the device or phone + number identification cannot be derived from the 3-legged access + token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: | + None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: | + An explicit identifier is provided when a device or phone + number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: | + Access to the API has been temporarily blocked due to rate or spike + arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedTokenAppId: + description: Empty JSON when device is identified by access token + value: + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + IdentifyDeviceByPhoneNumberAppId: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + + IdentifyDeviceByIPAddressAppEndpointsId: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + applicationEndpointsId: "4d596ac1-7822-4927-a3c5-d72e1f922c94" + + IdentifyDeviceByMultipleIdentifiersAppId: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" + appId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" diff --git a/original/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist.md b/original/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..9f9f5532b8f07445419e501e19d500e8935ef5ba --- /dev/null +++ b/original/ApplicationEndpointDiscovery/documentation/API_documentation/Application-Endpoint-Discovery-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# Application Endpoint Discovery API Readiness minimum criteria checklist + +Checklist for Application-Endpoint-Discovery v0.1.0 + +| Nr | API release assets | alpha | release-candidate | initial
                                                  public | stable
                                                  public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-endpoint-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y |[r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/SupportingDocuments/API_Documentation/User%20Stories/Application%20Endpoint%20Discovery%20User%20Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-endpoint-discovery.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.MD) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/137166903/ApplicationEndpointDiscovery+API+description) | diff --git a/original/ApplicationEndpointDiscovery/documentation/API_documentation/README.MD b/original/ApplicationEndpointDiscovery/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationEndpointDiscovery/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story.md b/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..fab29bfe62ccc4db9a78bc072fd693202ce9ebe1 --- /dev/null +++ b/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/API_Documentation/User_Stories/Application_Endpoint_Discovery_User_Story.md @@ -0,0 +1,84 @@ +# Application Endpoint Discovery API User Story + +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)_ + +| **Item** | **Details** | +| ---- | ------- | +| **_Summary_** | As an application developer belonging to an enterprise, I want to discover (using either my application server/backend service, or an HTTP application client on the end-user device) the optimal application instance running in an Edge Cloud Zone that a given end-user's device can connect to. | +| **_Roles and Actors and Scope_** | **Roles:** Customer:User
                                                  **Actors:** Application service providers, network operators, application developers. The API allows a check to see if end-user consent is required: if consent is required, the end-user will be an actor in the consent flow.
                                                  **Scope:** Get the endpoint of the application hosted at the optimal Edge Cloud Zone | +| **_Pre-conditions_** |The preconditions are listed below:
                                                  1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                  2. The Customer:BusinessManager has successfully subscribed to the Application Endpoint Discovery product from the product catalog.
                                                  3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                  4. The Customer:User has obtained a valid identifier for the target device, or, will make the API request from an application client on a device connected to the operator's network.
                                                  5. | +| **_Begins when_** | The customer application server/client makes a POST request to the Application Endpoint Discovery API to query the optimal Application Endpoint to the target device (an end-user device). The target device is either identified either in a 3-legged consent flow including a device object, or by device identifier(s) in the request body.| +| **_Ends when_** | The Application Endpoint Discovery API returns the endpoint(s) of the optimal application instance(s) for this user.| +| **_Post-conditions_** | Optional - the customer may decide to act upon the information by connecting the end-user application client to the application server instance hosted at one of the received Application Endpoints. | +| **_Exceptions_** | Several exceptions might occur during the API operations:
                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                    - Incorrect input data (e.g., malformed phone number).
                                                    - Not found: The phone number is not associated with a CSP customer account, the application does not have any running instances in the Edge Cloud, or the application endpoint ID received in the request is not registered in the Edge Cloud. | + +## API Workflows + +### Scenario 1: direct request from application client or end-user device + +Constraints: + +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: browser or app calls API over HTTPS +- Northbound Interface only (no 'UNI' client SDK required) +- The call must include an application identifier (_appId_) which must be provided by the Application Provider. + +Note: + +- the Edge Cloud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + autonumber + participant Application Client + participant Operator + participant Edge Cloud Zone + Note over Application Client, Operator: PRE developer has acquired an identifier for the device in question + Note over Application Client, Operator: PRE App developer registered, authenticated and authorised + Note over Application Client, Operator: PRE Application instances are up and running on one or several Edge Cloud Zones + + Application Client->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), appId}` + Operator->>Operator: Calculate optimal Application Endpoint(s) + Operator->>Application Client: optimal Application Endpoint(s) + opt connect to optimal instance endpoint + Application Client->>Edge Cloud Zone: Connect to optimal instance endpoint + end +``` + +### Scenario 2: request from developer server + +Constraints: + +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: none, browser or app calls API over HTTPs (no client SDK required) +- Dependencies: + - the call must include an identifier for the device (device) for which 'optimal MEC' is being calculated + - the call must include an application identifier: + - _appId_ (application identifier) in case the application is deployed by Edge Application Management API + - _applicationEndpointsId_ (registered endpoints identifier) for other cases. It requires previous registration of application endpoints using Application Endpoint Registration API. + +Note: the Edge CLoud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + autonumber + participant Application Client + participant Application Server + participant Operator + participant Edge Cloud Zone + Note over Application Server, Operator: PRE developer has acquired an identifier for the device in question + Note over Application Server, Operator: PRE App developer registered, authenticated and authorised + Note over Application Server, Operator: PRE Application instances are up and running on one or several Edge Cloud Zones + alt The application has been deployed with Edge Application Management API + Application Server->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), appId}` + else The application has not been instantiated with Edge Application Management API + Note over Application Server,Operator: PRE Application Endpoints have been registered in Operator Platform + Application Server->>Operator: POST request `/retrieve-optimal-app-endpoints {RequestBody: device identifier(s), applicationEndpointsId}` + end + Operator->>Operator: Calculate optimal Application Endpoint(s) + Operator->>Application Server: optimal Application Endpoint(s) + opt inform app so it connects to the instance endpoint + Application Server->>Application Client: report optimal Application Endpoint + Application Client->>Edge Cloud Zone: Connect to instance endpoint + end +``` diff --git a/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README.MD b/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationEndpointDiscovery/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationEndpointRegistration/README.md b/original/ApplicationEndpointRegistration/README.md new file mode 100644 index 0000000000000000000000000000000000000000..e403cfdbd6e6b5de4aa27283959605ca217763cd --- /dev/null +++ b/original/ApplicationEndpointRegistration/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationEndpointRegistration + +Sandbox API Repository to describe, develop, document, and test the ApplicationEndpointRegistration Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAsC) + +## Scope + +* Service API(s) “ApplicationEndpointRegistration” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * register the endpoints of an application which is deployed across various Edge Cloud Zones +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationEndpointRegistration/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-endpoint-registration v0.1.0** + [[YAML]](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/r1.2/code/API_definitions/application-endpoint-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointRegistration/r1.2/code/API_definitions/application-endpoint-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationEndpointRegistration/r1.2/code/API_definitions/application-endpoint-registration.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationEndpointRegistration/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationEndpointRegistration/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ApplicationEndpointRegistration/code/API_definitions/README.MD b/original/ApplicationEndpointRegistration/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/ApplicationEndpointRegistration/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration.yaml b/original/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e0bee4a5665745ae84b1d0c05e484dd4c4254e83 --- /dev/null +++ b/original/ApplicationEndpointRegistration/code/API_definitions/application-endpoint-registration.yaml @@ -0,0 +1,759 @@ +--- +openapi: 3.0.3 +info: + title: Application Endpoints Registration + version: wip + x-camara-commonalities: 0.6 + description: | + The Application Endpoints Registration API provides a programmable + interface for developers to register the endpoints of an application + which is deployed across various Edge Cloud Zones. + It allows developers to retrieve, update, and delete those registrations. + + # Introduction + + The API registers the Application Endpoints. + This information can be used for various use cases like optimal endpoint + discovery to help end users connect to the most optimal instance of the + application which is distributed across various Edge Cloud Zones. + Additionally the information can be used to monitor the edge instances to + take decisions from a lifecycle management perspective. The API provides + the ability to register, read and manage the deployed edge instances of + the application. + + # Relevant terms and definitions + + * **Application Endpoint**: + + The Endpoint on which the application is accessible. + It can be a FQDN, IPv4, or IPv6 address with a port number. + + * **Application Profile**: + + It represents the application's network and + compute characteristics. This helps distinguish between different + applications and their specific requirements. + + * **Edge Cloud Zone**: + + Availability Zone in an Edge Cloud. It is the lowest + level of abstraction exposed to an Application Provider who wants to + deploy an Application on Edge Cloud. Availability Zones exist within + a Region. + + # API functionality + + The API provides the following operations: + - POST registerApplicationEndpoints: Registers the Application Endpoints + of a deployed application to a specified edge cloud zone. + - GET getAllRegisteredApplicationEndpoints: Returns endpoint information for + all registered Applications. + - GET getApplicationEndpointsByID: Returns endpoint information for all + Applications registered to a specified applicationEndpointListId. + - PUT updateApplicationEndpoint: Update registered application endpoint + information. + - DELETE deregisterApplicationEndpoint: Deregister an application's + Endpoints. + ## Errors + + - If the API call contains a formatting or any other syntactic error, + a `400 INVALID_ARGUMENT` error is returned. + - If the API call cannot be authenticated due to missing, invalid, or + expired credentials, a `401 UNAUTHENTICATED` error is returned. + - If the API call has a valid access token that does not have the + required scope, then a `403 PERMISSION_DENIED` error is returned. + - If the API call has an `applicationEndpointListId` that does not identify + any registered endpoint on the Edge Cloud, a `404 NOT_FOUND` error + is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Further info and support + + [GSMA Mobile Connect Account Takeover Protection specification] + (https://www.gsma.com/identity/wp-content/uploads/2022/12/IDY.24-Mobile- + Connect-Account-Takeover-Protection-Definition-and-Technical-Requirements- + v2.0.pdf) + was used as source of input for this API. For more about Mobile Connect, + please see [Mobile Connect website](https://mobileconnect.io/). + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/ApplicationEndpointRegistration + +servers: + - url: "{apiRoot}/application-endpoint-registration/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application Endpoint Registration + description: | + Operations to register, read and manage deployed instances of the + application. + +paths: + /application-endpoint-lists: + post: + security: + - openId: + - application-endpoint-registration:application-endpoints:write + tags: + - Application Endpoint Registration + summary: Register endpoints of a deployed application + description: | + Register the endpoints of a deployed application + to a specified edge cloud zone. + operationId: registerApplicationEndpoints + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Array of Application Endpoints for an + application deployed across various Edge Cloud Zones. + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + responses: + "200": + description: Returns an applicationEndpointListId + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointListId" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - application-endpoint-registration:application-endpoints:read + tags: + - Application Endpoint Registration + summary: Get all registered edge application endpoint information + description: | + Returns endpoint information for all + registered Applications. + operationId: getAllRegisteredApplicationEndpoints + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Array of registered Application Endpoints + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/ApplicationEndpointList" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + "/application-endpoint-lists/{applicationEndpointListId}": + parameters: + - name: applicationEndpointListId + in: path + description: The unique identifier for the application endpoints + that got created when registering the application endpoints. + required: true + schema: + $ref: "#/components/schemas/ApplicationEndpointListId" + - $ref: "#/components/parameters/x-correlator" + get: + security: + - openId: + - application-endpoint-registration:application-endpoints:read + tags: + - Application Endpoint Registration + summary: Get registered edge application endpoint information + description: | + Returns endpoint information of the application based on + applicationEndpointListId. + operationId: getApplicationEndpointsById + responses: + "200": + description: Application Endpoint information based on + given ApplicationEndpointListID + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointList" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + put: + security: + - openId: + - application-endpoint-registration:application-endpoints:update + tags: + - Application Endpoint Registration + summary: Update an application Endpoint + description: | + Update registered application Endpoint information. + operationId: updateApplicationEndpoint + requestBody: + description: Application Endpoint information + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + responses: + "204": + description: Updates Application Endpoint Information + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + delete: + security: + - openId: + - application-endpoint-registration:application-endpoints:delete + tags: + - Application Endpoint Registration + summary: Deregister an application Endpoint + description: | + Deregister an application's + Endpoint from the edge cloud zone. + operationId: deregisterApplicationEndpoint + responses: + "204": + description: Deregister Application Endpoint + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + ApplicationEndpointsInfo: + description: Endpoint information of the Application + deployed across different Edge Cloud Zones. + type: object + properties: + applicationEndpoints: + type: array + description: List of endpoints of the application deployed across + various Edge Cloud Zones + items: + $ref: "#/components/schemas/ApplicationEndpoint" + applicationProviderName: + type: string + description: Name of the Application Provider + example: "AppProvider" + applicationDescription: + type: string + description: Description of the application. + example: "This is a V2X application." + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + required: + - applicationEndpoints + - applicationProviderName + - applicationProfileId + example: + applicationEndpoints: + - domainName: "app.example.com" + port: 8080 + applicationEndpointDescription: "V2X app deployed at ZoneA" + edgeCloudZone: + edgeCloudZoneId: "123e4567-e89b-12d3-a456-426614174000" + edgeCloudZoneName: "ZoneA" + edgeCloudProvider: "ProviderA" + edgeCloudRegion: "us-west-1" + edgeCloudZoneStatus: "active" + applicationProviderName: "AppProvider" + applicationDescription: "This is a V2X application." + applicationProfileId: "123e4567-e89b-12d3-a456-426614174000" + + ApplicationEndpointList: + type: object + description: | + List of Application endpoints information + deployed across various cloud zones. + required: + - applicationEndpointListId + - applicationEndpointsInfo + properties: + applicationEndpointListId: + $ref: "#/components/schemas/ApplicationEndpointListId" + applicationEndpointsInfo: + $ref: "#/components/schemas/ApplicationEndpointsInfo" + + ApplicationEndpoint: + type: object + description: | + An application server IP address or FQDN with a port, + exposed by an application instance deployed on the Edge Cloud + Zone. + required: + - port + anyOf: + - required: [domainName] + - required: [ipv4Address] + - required: [ipv6Address] + properties: + domainName: + $ref: "#/components/schemas/DomainName" + ipv4Address: + $ref: "#/components/schemas/SingleIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/SingleIpv6Addr" + port: + $ref: "#/components/schemas/Port" + edgeCloudZone: + $ref: "#/components/schemas/EdgeCloudZone" + applicationEndpointDescription: + type: string + description: Description of the application endpoint + example: "V2X app deployed at ZoneA" + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + + EdgeCloudZoneId: + description: A unique identifier for the Edge Cloud Zone. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + EdgeCloudRegion: + description: | + The EdgeCloudProvider's name for the region where the Edge Cloud + Zone is located. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + EdgeCloudProvider: + description: The provider of the Edge Cloud. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ProviderA" + + EdgeCloudZoneName: + description: The name of the Edge Cloud Zone. + type: string + pattern: ^[A-Za-z0-9]([A-Za-z0-9-]{0,53}[A-Za-z0-9])?$ + example: "ZoneA" + + ApplicationEndpointListId: + description: | + A system-defined string identifier representing + one or more registered Application Endpoints. This ID is generated + by the system upon successful registration of an application and is + used to reference the registered endpoints in subsequent operations. + type: string + format: uuid + readOnly: true + additionalProperties: false + example: "98765432-e89b-12d3-a456-426614174999" + + ApplicationProfileId: + description: | + A unique identifier for the application profile. This represents + the application's network and compute characteristics. + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + DomainName: + type: string + description: | + Application's Domain Name, which is a Fully Qualified Domain Name (FQDN). + pattern: ^[a-zA-Z0-9]([a-zA-Z0-9\-]{0,61}[a-zA-Z0-9])?(\.[a-zA-Z0-9]([a-zA-Z0-9\-]{0,61}[a-zA-Z0-9])?)+$ + maxLength: 253 + minLength: 4 + example: "app.example.com" + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + SingleIpv6Addr: + description: | + Single IPv6 address with no subnet mask + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: | + TCP or UDP port number for the application endpoint. + Valid range is 0-65535. + type: integer + minimum: 0 + maximum: 65535 + example: 8080 + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, + request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter + criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions + to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - UNIDENTIFIABLE_APPLICATION_PROFILE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier. + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: Service not supported for this applicationProfileId + UNIDENTIFIABLE_APPLICATION_PROFILE: + description: | + The Application Profile is not included in the request + and the profile information cannot be derived + from the 3-legged access token + value: + status: 422 + code: UNIDENTIFIABLE_APPLICATION_PROFILE + message: The Application Profile cannot be identified + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business + quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to + rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist.md b/original/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..da8dd76644b09128cdf10a4a14248ebe0fef01a1 --- /dev/null +++ b/original/ApplicationEndpointRegistration/documentation/API_documentation/Application-Endpoint-Registration-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# Application Endpoints Registration API Readiness minimum criteria checklist + +Checklist for Application-Endpoint-Registration v0.1.0 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-endpoint-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/application-endpoint-registration-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-endpoint-registration.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/dAAsC) | diff --git a/original/ApplicationEndpointRegistration/documentation/API_documentation/README.MD b/original/ApplicationEndpointRegistration/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationEndpointRegistration/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story.md b/original/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..a075f82416ed0b9003a03c9760f04c7165622def --- /dev/null +++ b/original/ApplicationEndpointRegistration/documentation/API_documentation/application-endpoint-registration-User-Story.md @@ -0,0 +1,10 @@ +# Application Endpoint Registration API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer who has deployed my application across multiple Edge Cloud Zones, I need a way to register and manage the endpoints of my application instances. The Application Endpoint Registration API allows me to register my application endpoints across different Edge Cloud Zones, update their information when necessary, retrieve endpoint details, and remove endpoints when they are decommissioned. This registration process enables the discovery of these endpoints through the Application Endpoint Discovery API, ensuring users can connect to the optimal instance of my application. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
                                                    **Actors:** Application service providers, hyperscalers, application developers
                                                    **Scope:**
                                                    • Register application endpoints in various Edge Cloud Zones
                                                    • Update existing application endpoint information
                                                    • Retrieve application endpoint details
                                                    • Delete application endpoints when no longer needed
                                                    | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
                                                    2. The API Consumer:BusinessManager has successfully subscribed to the Application Endpoint Registration product from the product catalog.
                                                    3. The API Consumer:Administrator has onboarded the developer:User to the platform.
                                                    4. The API Consumer has deployed application instances across various Edge Cloud Zones and has the necessary information about each endpoint.
                                                    5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.
                                                    | +| ***Activities/Steps*** | **Starts when:**
                                                    1. The API consumer application server makes requests to:
                                                    - Register a new application endpoint by providing endpoint details.
                                                    - Retrieve information about a specific registered endpoint.
                                                    - Update the details of an existing registered endpoint.
                                                    - Delete a registered endpoint that is no longer active.

                                                    **Ends when:**
                                                    1. The API endpoint successfully processes the registration, update, retrieval, or deletion request. | +| ***Post-conditions*** | 1. For registration: A new application endpoint is registered and available for discovery.
                                                    2. For update: The application endpoint information is updated with the latest details.
                                                    3. For retrieval: The current information about the application endpoint is provided.
                                                    4. For deletion: The application endpoint is removed from the registration system and will no longer be discoverable. | +| ***Exceptions*** | Several exceptions might occur
                                                    - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                    - Invalid input: Not valid input data to register or update an endpoint (e.g. malformed URI).
                                                    - Conflict: An endpoint with the same identifier already exists during registration.
                                                    - Not Found: The requested endpoint doesn't exist during retrieval, update, or deletion operations. | diff --git a/original/ApplicationEndpointRegistration/documentation/SupportingDocuments/README.MD b/original/ApplicationEndpointRegistration/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationEndpointRegistration/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationProfiles/README.md b/original/ApplicationProfiles/README.md new file mode 100644 index 0000000000000000000000000000000000000000..6387f66f2b6111fba987aa6bac953d8574905d56 --- /dev/null +++ b/original/ApplicationProfiles/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# ApplicationProfiles + +Sandbox API Repository to describe, develop, document, and test the ApplicationProfiles Service API(s) within the context of [ConnectivityInsights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14561833/ConnectivityInsights) + +* API Repository [Wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mgGaBQ) + +## Scope + +* Service API(s) “ApplicationProfiles” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Application profiles allows application developers to share all the information about their application which would be relevant for network CAMARA APIs related decision making. +* Describe, develop, document, and test the API(s) +* Started: October 2024 (within ConnectivityInsights, own repository since March 2025) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ApplicationProfiles/releases/tag/r1.2) (Fall25), with the following API versions: + * **application-profiles v0.5.0** + [[YAML]](https://github.com/camaraproject/ApplicationProfiles/blob/r1.2/code/API_definitions/application-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ApplicationProfiles/r1.2/code/API_definitions/application-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ApplicationProfiles/r1.2/code/API_definitions/application-profiles.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ApplicationProfiles/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ApplicationProfiles/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ApplicationProfiles/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually together with ConnectivityInsights + * Schedule: Bi-weekly on Wednesday at 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vzve) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ApplicationProfiles/code/API_definitions/README.MD b/original/ApplicationProfiles/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/ApplicationProfiles/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/ApplicationProfiles/code/API_definitions/application-profiles.yaml b/original/ApplicationProfiles/code/API_definitions/application-profiles.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fbed98a3d7ec128d68d132642ee5a0ecb028fb1f --- /dev/null +++ b/original/ApplicationProfiles/code/API_definitions/application-profiles.yaml @@ -0,0 +1,683 @@ +openapi: 3.0.3 +info: + title: Connectivity Insights - Application Profiles + x-camara-commonalities: 0.6 + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + description: | + Application profiles allow developers to specify all relevant information about their application for both network and compute resource + requirements,supporting CAMARA APIs and network decision making. + + This API enables defining, reading, and managing application requirements,including: + - Network quality thresholds (latency, jitter, loss, throughput) + - Compute resource thresholds (CPU, GPU, memory, storage) + + The information captured as part of application profiles can be used in different usecases for decision making. Please refer connectivity insights and session insights for more details as a reference to see how the information in application profiles is used for decision making. + The scope will expand as new requirements from CAMARA APIs emerge. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) for the + released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local + legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + contact: + email: sp-edc@lists.camaraproject.org +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/ApplicationProfiles +servers: + - url: "{apiRoot}/application-profiles/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application Profiles + description: | + Operations to define, read and manage an application's thresholds + for network quality (latency, jitter, loss, throughput) + +paths: + /application-profiles: + post: + security: + - openId: + - application-profiles:create + tags: + - Application Profiles + summary: Create an Application Profile + description: | + Define network monitoring intents for optimal end user application + experience. + operationId: createApplicationProfile + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: List of user-defined network quality thresholds + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfileRequest" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + + /application-profiles/{applicationProfileId}: + patch: + security: + - openId: + - application-profiles:update + tags: + - Application Profiles + summary: Update an Application Profile + description: | + Update the complete set of network quality thresholds for an + application with the new set of thresholds to ensure good + end user experience + operationId: updateApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: | + network monitoring intents for optimal end user application + experience. + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + required: true + responses: + "200": + description: OK + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + get: + security: + - openId: + - application-profiles:read + tags: + - Application Profiles + summary: Get an Application Profile + description: Read an Application Profile + operationId: readApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + content: + application/json: + schema: + $ref: "#/components/schemas/ApplicationProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + delete: + security: + - openId: + - application-profiles:delete + tags: + - Application Profiles + summary: Delete an Application Profile + description: Delete an application profile + operationId: deleteApplicationProfile + parameters: + - name: applicationProfileId + in: path + description: Identifier for the Application Profile + required: true + style: simple + explode: false + schema: + type: string + format: uuid + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Application profile has been deleted successfully. + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + Duration: + type: object + properties: + value: + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + allOf: + - $ref: "#/components/schemas/TimeUnitEnum" + - example: Minutes + + TimeUnitEnum: + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + Rate: + type: object + properties: + value: + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + type: string + enum: + - Bps + - Kbps + - Mbps + - Gbps + - Tbps + + Compute: + type: object + properties: + value: + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/ComputeUnitEnum" + + ComputeUnitEnum: + type: string + enum: + - Kb + - Mb + - Gb + - Tb + + PacketDelayBudget: + description: | + The packet delay budget is the maximum allowable one-way latency + between the customer's device and the gateway from the operator's + network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, + such as voice calls, video streaming, and data. The end-to-end or + round trip latency will be about two times this value plus the latency + not controlled by the operator + allOf: + - $ref: "#/components/schemas/Duration" + + PacketErrorLossRate: + type: integer + description: + The exponential power of the allowable error loss rate 10^(-N). + For instance 3 would be an error loss rate of 10 to the power of -3 + (0.001) + + For 5G network the 3GPP specification TS 23.203 defines the packet + error loss rate QCI attribute. It describes the Quality of Service + (QoS) Class Identifier (QCI) parameters used to differentiate traffic + classes in mobile networks, ensuring appropriate resource + allocation and performance for various services. + + The packet error loss rate is one of the QCI attributes, providing + information on the acceptable packet loss rate for a specific traffic + class. This attribute helps maintain the desired performance level for + services like voice calls, video streaming, or data transfers within + the 3GPP mobile network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + + Jitter: + description: + The jitter requirement aims to limit the maximum variation in + round-trip packet delay for the 99th percentile of traffic, following + ITU Y.1540 standards. It considers only acknowledged packets in a + session, which are packets that receive a confirmation of receipt from + the recipient (e.g., using TCP). This requirement helps maintain + consistent latency, essential for real-time applications such as VoIP, + video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + + TargetMinDownstreamRate: + description: | + This is the target minimum downstream rate. + allOf: + - $ref: "#/components/schemas/Rate" + + TargetMinUpstreamRate: + description: | + This is the target minimum upstream rate. + allOf: + - $ref: "#/components/schemas/Rate" + + targetMinCPU: + type: number + description: + Number of vCPUs required for the application. Fractional values are allowed (e.g., 0.5 = half a vCPU). The value represents the minimum amount of CPU resources to be allocated to the application instance. + example: 0.5 + + targetMinGPU: + description: | + This is the target minimun GPUs required by the application + format: integer + example: 1 + + gpuVendorType: + type: string + enum: + - Nvidia + - AMD + description: GPU vendor name e.g. NVIDIA, AMD etc. + example: Nvidia + + gpuModelName: + type: string + description: Model name corresponding to vendorType may include info e.g. for NVIDIA, model name could be “Tesla M60”, “Tesla V100” etc. + + targetMinMemory: + description: | + This is the target minimum memory required by the application + allOf: + - $ref: "#/components/schemas/Compute" + + targetMinEphemeralStorage: + description: | + This is the target minimum ephemeral storage required by the application + allOf: + - $ref: "#/components/schemas/Compute" + + targetMinPersistentStorage: + description: | + This is the target minimum persistent storage required by the + application + allOf: + - $ref: "#/components/schemas/Compute" + + ApplicationProfile: + type: object + required: + - applicationProfileId + properties: + applicationProfileId: + type: string + format: uuid + networkQualityThresholds: + $ref: "#/components/schemas/NetworkQualityThresholds" + computeResources: + $ref: "#/components/schemas/ComputeResourcesThresholds" + anyOf: + - required: [networkQualityThresholds] + - required: [computeResources] + + ApplicationProfileRequest: + type: object + anyOf: + - required: [networkQualityThresholds] + - required: [computeResources] + properties: + networkQualityThresholds: + $ref: "#/components/schemas/NetworkQualityThresholds" + computeResources: + $ref: "#/components/schemas/ComputeResourcesThresholds" + + NetworkQualityThresholds: + type: object + properties: + packetDelayBudget: + $ref: "#/components/schemas/PacketDelayBudget" + targetMinDownstreamRate: + $ref: "#/components/schemas/TargetMinDownstreamRate" + targetMinUpstreamRate: + $ref: "#/components/schemas/TargetMinUpstreamRate" + packetLossErrorRate: + $ref: "#/components/schemas/PacketErrorLossRate" + jitter: + $ref: "#/components/schemas/Jitter" + minProperties: 1 + + ComputeResourcesThresholds: + type: object + properties: + targetMinCPU: + $ref: "#/components/schemas/targetMinCPU" + targetMinMemory: + $ref: "#/components/schemas/targetMinMemory" + gpuVendorType: + $ref: "#/components/schemas/gpuVendorType" + gpuModelName: + $ref: "#/components/schemas/gpuModelName" + targetMinGPU: + $ref: "#/components/schemas/targetMinGPU" + targetMinGPUMemory: + $ref: "#/components/schemas/targetMinMemory" + targetMinEphemeralStorage: + $ref: "#/components/schemas/targetMinEphemeralStorage" + targetMinPersistentStorage: + $ref: "#/components/schemas/targetMinPersistentStorage" + description: Compute resources of a Application Profile + minProperties: 1 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body + or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when + a given field has a pre-defined range or a invalid filter + criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not + have the required scope or when the user fails operational + security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business + quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due + to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/ApplicationProfiles/documentation/API_documentation/README.MD b/original/ApplicationProfiles/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationProfiles/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist.md b/original/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..496bd13fb73085e0b7ce6ed2bcb35edce621efc2 --- /dev/null +++ b/original/ApplicationProfiles/documentation/API_documentation/application-profiles-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for application-profiles v0.5.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/application-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/application-profiles-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/application-profiles.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/iQFmBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story.md b/original/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..9630f58b5ae4e2b2acdea73f06beb016ceb770ff --- /dev/null +++ b/original/ApplicationProfiles/documentation/API_documentation/application-profiles-User-Story.md @@ -0,0 +1,10 @@ +# Application profiles API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to share key details about my application that are relevant for network-related decisions across various CAMARA APIs. Specifically, I need to define, store, and manage my application's network quality thresholds (latency, jitter, packet loss, and throughput) that represent my application's networking demands. These thresholds will serve as a baseline for determining whether the network can provide adequate performance for my application's users | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
                                                    **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
                                                    **Scope:**
                                                    • Create and manage application profiles
                                                    • Perform network quality check againt the application profile for specific user sessions
                                                    • Create subscriptions to recieve notifications if the network is not able to meet the application's requirements
                                                    | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
                                                    2. The API Consumer:BusinessManager has successfully subscribed to the Application Profiles product from the product catalog.
                                                    3. The API Consumer:Administrator has onboarded the developer:User to the platform.
                                                    4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                                                    5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:**
                                                      1. The API consumer makes a POST request to /application-profiles with network quality thresholds including packetDelayBudget, targetMinDownstreamRate, targetMinUpstreamRate, packetlossErrorRate, and jitter.

                                                      **Additional Operatios:**
                                                      2. The API consumer can make a GET request to /application-profiles/{applicationProfileId} to retrieve an existing profile.
                                                      3. The API consumer can make a PATCH request to /application-profiles/{applicationProfileId} to update network quality thresholds for an existing profile.
                                                      4. The API consumer can make a DELETE request to /application-profiles/{applicationProfileId} to remove a profile that is no longer needed.

                                                      **Ends when:**
                                                      The application profile is either successfully created, updated, retrieved, or deleted based on the API consumer's request. | +| ***Post-conditions*** | 1. For POST: A new application profile is created with a unique applicationProfileId and the specified network quality thresholds.
                                                      2. For GET: The details of the requested application profile are returned to the API consumer.
                                                      3. For PATCH: The application profile is updated with the new network quality thresholds.
                                                      4. For DELETE: The application profile is removed from the system.| +| ***Exceptions*** | Several exceptions might occur
                                                      - Bad Request: Invalid argument or out-of-range values for network quality thresholds.
                                                      - Unauthorized: Invalid, missing, or expired access token.
                                                      - Forbidden: Insufficient permissions or invalid token context.
                                                      - Not Found: Requested application profile does not exist.
                                                      - Too Many Requests: Rate limit or quota exceeded.| diff --git a/original/ApplicationProfiles/documentation/SupportingDocuments/README.MD b/original/ApplicationProfiles/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ApplicationProfiles/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/BlockchainPublicAddress/README.md b/original/BlockchainPublicAddress/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9bab85dbc85d07d849388f2e1293f0e27b9a3c62 --- /dev/null +++ b/original/BlockchainPublicAddress/README.md @@ -0,0 +1,58 @@ + + + + + + + + + +# BlockchainPublicAddress + +Sandbox API Repository to describe, develop, document, and test the BlockchainPublicAddress Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KDHe) + +## Scope +* Service APIs for “Blockchain Public Address” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Blockchain Public Address API: + * Manage a Blockchain Public Address associated to a phone number, i.e. to retrieve the blockchain public address(es) and to bind/unbind a Blockchain Public Address. The Blockchain Public Address is utilized as Decentralized Identifier (DID). With the proposed API, API providers offer API consumers the following capability: pairing phone number with Blockchain Public Address whenever this 3rd party wants to offer its customers a way to make transactions more easily based on the phone number instead of the Blockchain Public Address. + * Optional binding enforcement procedure, ensuring both `phoneNumber` and `blockchainPublicAddress` belongs to the same owner (i.e. person), within binding process by means of the checking of provided `nonce` and `signature` fields. To generate `nonce` below mentioned Blockchain Public Address Validation API has been designed, and `signature` generation is an off-chain process. + * Blockchain Public Address Validation API: + * Manage generation of a nonce (one-time challenge) to be used in binding enforcemnet procedure. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: June 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/r2.2) (Fall25), with the following API versions: + * **blockchain-public-address-validation v0.1.0** + [[YAML]](https://github.com/camaraproject/BlockchainPublicAddress/blob/r2.2/code/API_definitions/blockchain-public-address-validation.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address-validation.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address-validation.yaml) + * **blockchain-public-address v0.3.0** + [[YAML]](https://github.com/camaraproject/BlockchainPublicAddress/blob/r2.2/code/API_definitions/blockchain-public-address.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/code/API_definitions/blockchain-public-address.yaml) +* The latest public release is always available here: https://github.com/camaraproject/BlockchainPublicAddress/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/BlockchainPublicAddress/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99023344259?password=cb995600-56ee-48a2-ade1-607bb10487df) + * Schedule: Bi-weekly on Thursdays, 13:00-14:00 CET/CEST (12:00 UTC, 11:00 UTC during European DST) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/thDe). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation.yaml b/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation.yaml new file mode 100644 index 0000000000000000000000000000000000000000..80d84e88c065005b0c0b4ee9d74b184bfc51c1b0 --- /dev/null +++ b/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address-validation.yaml @@ -0,0 +1,254 @@ +openapi: 3.0.3 +info: + title: Blockchain Public Address Validation + description: |- + This API allows the API consumer to generate a one-time nonce for Enhanced Binding validation for Blockchain Public Address associated with a mobile phone number. + + # Relevant Definitions and concepts + - **Blockchain Public Address**: Unique string of code used by individuals that can be used to send, receive, and store digital assets (e.g. payments in cryptocurrencies, smart contracts, NFT (Non-Fungible Tokens), etc.) on a blockchain network + to receive or request payments in cryptocurrency. + + # API Functionality + This API allows to generate a one-time nonce to allow for enhanced validation procedure for Blockchain Public Address binding associated with a mobile phone number, as per defined in `bindBlockchainPublicAddress` operation of CAMARA Blockchain Public Address API. + + # Resources and Operations overview + This API provides one endpoint: + - **Endpoint to generate a one-time nonce associated to a specific Blockchain Public Address**. It does not matter if the mobile phone number is already bound to a Blockchain Public Address, as this operation adds a new Blockchain Public Address. This operation MUST be used with a 3-legged Access Token + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further Info and Support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/BlockchainPublicAddress +servers: + - url: "{apiRoot}/blockchain-public-address-validation/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Blockchain Public Address Validation Nonce + description: API operations to manage Blockchain Public Address Validation Nonce +paths: + /nonce: + post: + tags: + - Blockchain Public Address Validation Nonce + summary: Generates a one-time nonce associated to a specific Blockchain Public Address + description: Generates a one-time nonce (i.e. challenge) associated to a specific Blockchain Public Address to allow for enhanced validation as per defined in `bindBlockchainPublicAddress` operation of CAMARA Blockchain Public Address API. + operationId: createBlockchainPublicAddressValidationNonce + security: + - openId: + - blockchain-public-address-validation:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBlockchainPublicAddressValidationNonce" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBlockchainPublicAddressValidationNonceResponse" + examples: + CreateBlockchainPublicAddressValidationNonceResponse201Example: + value: + nonce: "abc626ce-5284-4a84-b85e-46e0ee3d0434" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreateBlockchainPublicAddressValidationNonce: + type: object + description: Payload to request the nonce generation associated to a given Blockchain Public Address + required: + - blockchainPublicAddress + properties: + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address use for the latter binding to a specific `phoneNumber`. + example: + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + CreateBlockchainPublicAddressValidationNonceResponse: + type: object + description: Nonce generation associated to a given Blockchain Public Address response + required: + - nonce + properties: + nonce: + type: string + description: |- + One-time challenge generated associated to indicated `blockchainPublicAddress`. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address.yaml b/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address.yaml new file mode 100644 index 0000000000000000000000000000000000000000..17e14a05d63e3c077ded7e9c63507fdc9c682242 --- /dev/null +++ b/original/BlockchainPublicAddress/code/API_definitions/blockchain-public-address.yaml @@ -0,0 +1,659 @@ +openapi: 3.0.3 +info: + title: Blockchain Public Address + description: |- + This API allows the API consumer to manage Blockchain Public Address associated with a mobile phone number. + + # Relevant Definitions and concepts + - **Blockchain Public Address**: Unique string of code used by individuals that can be used to send, receive, and store digital assets (e.g. payments in cryptocurrencies, smart contracts, NFT (Non-Fungible Tokens), etc.) on a blockchain network + to receive or request payments in cryptocurrency. + + # API Functionality + This API allows the API consumer to manage a Blockchain Public Address associated with a mobile phone number, i.e.: to retrieve the Blockchain Public Address(es) and to bind/unbind a Blockchain Public Address. + + # Resources and Operations overview + This API provides three endpoints: + - **Endpoint to retrieve the Blockchain Public Address(es) associated with a mobile phone number sent as input**. The Blockchain Public Address is information made available by the user, in association to their mobile phone number. Then, this endpoint may be accessed in 2-legged or in 3-legged mode. Even in 3-legged mode, the mobile phone number included as input field does not need to belong to the `sub` (representing the User) for which the Access Token is issued. This will enable a user to ask for the Blockchain Public Address(es) of any mobile phone number, in order to perform a transaction with one of the available ones (send or request). + - **Endpoint to associate a mobile phone number with a Blockchain Public Address**. It does not matter if the mobile phone number is already bound to a Blockchain Public Address, as this operation adds a new Blockchain Public Address. This operation MUST be used with a 3-legged Access Token, and the indicated mobile phone number must belong to the `sub` (representing the User) in the Access Token; this is because only the user of the mobile phone number must be able to perform a bind. As a consequence, this operation will only work with mobile phone numbers of the Telco Operator exposing the API. + - **Endpoint to remove the association of a mobile phone number with a Blockchain Public Address**. This operation MUST be used with a 3-legged Access Token; this is because only the user of the mobile phone number must be able to perform an unbind. Note: Due to this, the API Server must validate that the `id` included in the request refers to a bind for a mobile phone number belonging to the `sub` (representing the User) in the Access Token. As a consequence, this operation will only work with mobile phone numbers of the Telco Operator exposing the API. + + ## Enforcement of the Blockchain Public Address ownership in binding process + + The enforcement of the Blockchain Public Address ownership in the binding process is optional, and it is not mandatory to use the `nonce` and `signature` fields. If the API consumer does not want to enforce this, it can simply omit these fields in the request body. + + This enforcement is aimed to ensure that the Blockchain Public Address being bound to a mobile phone number is indeed owned by the user (i.e. person behind) of that mobile phone number. + The API consumer can request the user to sign a `nonce` off-chain, and then include the `nonce` and `signature` in the request body when binding the Blockchain Public Address. The API Server will then verify that the `signature` is valid for the given `nonce` and `blockchainPublicAddress`. + + The E2E procedure is depicted in below picture: + ![Binding Enforcement - Off-Chain Signature](https://raw.githubusercontent.com/camaraproject/BlockchainPublicAddress/r2.2/documentation/API_documentation/resources/blockchain-public-address-binding-enforcement-off-chain-signature.png) + + LEGEND: + - `API Server`, `Challenge Module` and `Binding Database` are functional components that represent the underlying Backend API Logic in the Telco Operator. How this CAMARA API is implemented by a Telco Operator is out of scope of this specification. + + It comprises four steps: + - **(A) Obtain 3-Legged Access Token**: This is the regular process of obtaining a CAMARA 3-legged Access Token. CAMARA OIDC Authorization Code Flow is mentioned for illustrative purposes, other CAMARA 3-legged Access Token flows may be used. Check CAMARA Identity and Consent Management WG for details. + - **(B) Request a nonce from the API Server**: This is the feature provided by **_CAMARA Blockchain Public Address Validation Nonce API_**, allowing the API consumer to request a `nonce` associated to the `blockchainPublicAddress` to be signed by the user. + - **(C) Ask the user to sign the nonce off-chain**: The API consumer will use this `nonce` to ask the user to sign it off-chain. The user will sign the `nonce` using their private key. The API consumer will then obtain a `signature`, which is a cryptographic proof that the user owns the `blockchainPublicAddress`. + - **(D) Bind the Blockchain Public Address to the mobile phone number**: This step includes the `nonce` and `signature` in the request body. For signature validation, there are many options (e.g. https://ecrecover.org/, tools like `ethers.js` or `web3.js`); that is an implementation topic out of scope of this CAMARA API specification. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further Info and Support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/BlockchainPublicAddress +servers: + - url: "{apiRoot}/blockchain-public-address/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Blockchain Public Address + description: API operations to manage Blockchain Public Addresses +paths: + /blockchain-public-addresses/retrieve-blockchains: + post: + tags: + - Blockchain Public Address + summary: Retrieves Blockchain Public Address associated with a mobile phone number. + description: + Retrieves Blockchain Public Address associated with a mobile phone number. This operation can be accessed in 3-legged and in 2-legged, notice that the mobile phone number used as input need not be related with the user or mobile phone number to which the Access + Token is associated; this is because the operation is intended to be used to manage Blockchain Public Address of any mobile phone number, in order to perform send or request crypto operations. + operationId: retrieveBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + description: Array of Blockchain Public Addresses bound to the mobile phone number + items: + $ref: "#/components/schemas/BlockchainPublicAddressResponse" + examples: + RetrieveBlockchainPublicAddressResponse200Example: + value: + - id: "90c626ce-5284-4a84-b85e-46e0ee3d0434" + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + blockchainNetworkId: "evm:1" + currency: + - ETH + - id: "5c179f50-db37-4d23-87e3-6f10c991899f" + blockchainPublicAddress: "0x329CdCAAC31c934fe32322b111bE8fBd30b4FFA9" + blockchainNetworkId: "evm:137" + currency: + - WETH + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /blockchain-public-addresses: + post: + tags: + - Blockchain Public Address + summary: Binds Blockchain Public Address to a mobile phone number + description: + Binds Blockchain Public Address to a mobile phone number. If the mobile phone number is already bound to a Blockchain Public Address, this operation will add a new bound Blockchain Public Address to the mobile phone number. This operation is intended to be used + with a 3-legged Access Token, and the indicated mobile phone number must belong to the user identified by its `sub` in the Access Token; this is because only the user of the mobile phone number must be able to perform the bind. + + Specifically for this functionality, when a binding operation indicates a `blockchainNetworkId` not allowed by Telco Operator exception `403 - BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED` will be generated. + operationId: bindBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/BindBlockchainPublicAddressRequest" + required: true + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BindBlockchainPublicAddressResponse" + examples: + BindBlockchainPublicAddressResponse201Example: + value: + id: "90c626ce-5284-4a84-b85e-46e0ee3d0434" + "400": + $ref: "#/components/responses/InvalidArgumentForBlockchain400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PermissionDeniedForBlockchain403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /blockchain-public-addresses/{id}: + delete: + tags: + - Blockchain Public Address + summary: Unbinds Blockchain Public Address association to a mobile phone number + description: |- + Unbinds Blockchain Public Address to a mobile phone number. This operation is intended to be used with a 3-legged Access Token; this is because only the user of the mobile phone number must be able to perform the unbind. + Note: Due to this, the API Server must validate that the `id` included in the request refers to a bind for a mobile phone number belonging to the user identified by its `sub` in the Access Token. + operationId: deleteBlockchainPublicAddress + security: + - openId: + - blockchain-public-address:delete + parameters: + - $ref: "#/components/parameters/Id" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: No Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Id: + name: id + in: path + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + required: true + schema: + type: string + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: object + description: Payload to retrieve the Blockchain Public Address(es) associated to a given Phone Number + required: + - phoneNumber + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + BindBlockchainPublicAddressRequest: + type: object + description: Payload to request the Bind of the Blockchain Public Address + required: + - phoneNumber + - blockchainPublicAddress + - blockchainNetworkId + properties: + phoneNumber: + type: string + description: Mobile phone number to which the Blockchain Public Address will be bound. A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address to bind to the mobile `phoneNumber` + blockchainNetworkId: + type: string + pattern: ^[a-zA-Z0-9]+:?[a-zA-Z0-9]+$ + description: |- + Identifier (i.e. name/type) of the blockchain whose address value is provided within `blockchainPublicAddress`. The model proposed aims to provide an extensible way to list/identify every blockchain ecosystems. + Proposed format is: `:`, where: + + - ``: Represents a Layer 1 Blockchain Ecosystem (e.g. ethereum, bitcoin,...) + - ``: Represents subsequents L2 and Testnet Blockchain Ecosystems, whenever they apply (e.g. bitcoin is a monolithic blockchain so as this concept does not apply) + + So far, in the scope of v0.2 of this specification, the following `` values are covered: + - `evm`: Representing a common L1 Layer concept for EVM-based networks. Within this Ecosystem, `` concept is required and matches the value of chainId as per [EVM ChainId](https://chainid.network/). For instance: + - `ethereum` blockchain would be identified by `evm:1` value (i.e. ethereum mainnet). + - `polygon` blockchain would be identified by `evm:137` value (i.e. polygon mainnet). + - `celo` blockchain would be identified by `evm:42220` value (i.e. celo mainnet). + - `aleph zero` blockchain would be identified by `evm:41455` value (i.e. aleph zero evm). + - `bitcoin`: Representing Bitcoin L1 blockchain. No `` concept applies for this L1 Ecosystem + - `solana`: Representing Solana L1 blockchain. No `` concept applies for this L1 Ecosystem + - `cardano`: Representing Cardano L1 blockchain. No `` concept applies for this L1 Ecosystem + currency: + type: array + description: List of currencies for the blockchain. Optional field (generally not needed), only indicated when there are business needs to set one or a list on currencies supported. + minItems: 0 + items: + type: string + nonce: + type: string + description: |- + One-time challenge generated by means of endpoint `createBlockchainPublicAddressValidationNonce` of CAMARA API Blockchain Public Address Challenge. + + It is used along with `signature` to perform optional enhanced enforcement to ensure blockChainPublicAddress can be associated to the phoneNumber as it belongs to the owner of the blockChainPublicAddress. + signature: + type: string + description: |- + Unique distinctive generated as a result of asking the user to sign the nonce off-chain. + + It is used along with `nonce` to perform optional enhanced enforcement to ensure blockChainPublicAddress can be associated to the the phoneNumber as it belongs to the owner of the blockChainPublicAddress. + example: + phoneNumber: "+346789990012" + blockchainPublicAddress: "0x71C7656EC7ab88b098dafB451B2314C5f6d8932A" + blockchainNetworkId: "evm:1" + currency: + - ETH + BindBlockchainPublicAddressResponse: + type: object + description: Bind Blockchain Public Address response + required: + - id + properties: + id: + type: string + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + BlockchainPublicAddressResponse: + type: object + description: Blockchain Public Address response + required: + - id + - blockchainPublicAddress + - blockchainNetworkId + properties: + id: + type: string + description: Unique identifier given to the bind relationship of a mobile `phoneNumber` with a Blockchain Public Address. + blockchainPublicAddress: + type: string + description: User's Blockchain Public Address + blockchainNetworkId: + type: string + description: |- + Identifier (i.e. name/type) of the blockchain whose address value is provided within `blockchainPublicAddress`. The model proposed aims to provide an extensible way to list/identify every blockchain ecosystems. + Proposed format is: `:`, where: + - ``: Represents a Layer 1 Blockchain Ecosystem (e.g. ethereum, bitcoin,...) + - ``: Represents subsequents L2 and Testnet Blockchain Ecosystems, whenever they apply (e.g. bitcoin is a monolithic blockchain so as this concept does not apply) + + So far, in the scope of v0.2 of this specification, the following `` values are covered: + - `evm`: Representing a common L1 Layer concept for EVM-based networks. Within this Ecosystem, `` concept is required and matches the value of chainId as per [EVM ChainId](https://chainid.network/). For instance: + - `ethereum` blockchain would be identified by `evm:1` value (i.e. ethereum mainnet). + - `polygon` blockchain would be identified by `evm:137` value (i.e. polygon mainnet). + - `celo` blockchain would be identified by `evm:42220` value (i.e. celo mainnet). + - `aleph zero` blockchain would be identified by `evm:41455` value (i.e. aleph zero evm). + - `bitcoin`: Representing Bitcoin L1 blockchain. No `` concept applies for this L1 Ecosystem + - `solana`: Representing Solana L1 blockchain. No `` concept applies for this L1 Ecosystem + - `cardano`: Representing Cardano L1 blockchain. No `` concept applies for this L1 Ecosystem + currency: + type: array + description: List of currencies for the blockchain. Optional field (generally not needed), only indicated when there are business needs to set one or a list on currencies supported. + minItems: 0 + items: + type: string + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + InvalidArgumentForBlockchain400: + description: | + Problem with the client request. + In addition to regular scenario of INVALID_ARGUMENT, other exceptions may exist. + - Indicated blockchainNetworkId is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER","message": "Indicated blockchainNetworkId is not valid") + - Indicated currency is not valid for the Blockchain ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY","message": "Indicated currency is not found") + - Currency indication is required ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED","message": "One currency is required") + - Indicated nonce is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE","message": "Indicated nonce is not valid") + - Indicated signature is not valid ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE","message": "Indicated signature is not valid") + - Both nonce and signature are required together to perform enhanced validation ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED","message": "Both nonce and signature are required for enhanced validation") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY + - BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE + - BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE + - BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_BLOCKCHAIN_NETWORK_ID: + description: blockchainNetworkId is not valid + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_BLOCKCHAIN_NETWORK_IDENTIFIER + message: Indicated blockchainNetworkId is not valid + GENERIC_400_INVALID_CURRENCY_FOR_BLOCKCHAIN: + description: Invalid currency + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_CURRENCY + message: Indicated currency is not found + GENERIC_400_REQUIRED_CURRENCY_FOR_BLOCKCHAIN: + description: Currency is required + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.CURRENCY_REQUIRED + message: One currency is required + GENERIC_400_INVALID_NONCE: + description: Invalid nonce + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_NONCE + message: Indicated nonce is not valid + GENERIC_400_INVALID_SIGNATURE: + description: Invalid signature + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.INVALID_SIGNATURE + message: Indicated signature is not valid + GENERIC_400_BOTH_NONCE_SIGNATURE_REQUIRED: + description: Both nonce and signature are required together + value: + status: 400 + code: BLOCKCHAIN_PUBLIC_ADDRESS.BOTH_NONCE_SIGNATURE_REQUIRED + message: Both nonce and signature are required for enhanced validation + PermissionDeniedForBlockchain403: + description: | + Forbidden. + In addition to regular scenario of PERMISSION_DENIED, other exceptions may exist. + - Blockchain identifier not allowed by business rules ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED","message": "Indicated blockchainNetworkId is not allowed by business rules") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_NOT_ALLOWED_BLOCKCHAIN_NETWORK_ID: + description: blockchainNetworkId not allowed by business rules + value: + status: 403 + code: BLOCKCHAIN_PUBLIC_ADDRESS.BLOCKCHAIN_NETWORK_IDENTIFIER_NOT_ALLOWED + message: Indicated blockchainNetworkId is not allowed by business rules + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic422: + description: |- + Unprocessable content. + - Enhanced Binding validation procedure by means of nonce and signature verification is not supported ("code": "BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION","message": "Enhanced Binding validation procedure is not supported") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION + examples: + GENERIC_422_UNSUPPORTED_ENHANCED_VALIDATION: + description: Enhanced Binding validation procedure by means of nonce and signature verification is not supported + value: + status: 422 + code: BLOCKCHAIN_PUBLIC_ADDRESS.UNSUPPORTED_ENHANCED_VALIDATION + message: Enhanced Binding validation procedure is not supported + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist.md b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..2df270ed69fe48e52b944f5bf83d79fa9aa2ed48 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for BlockChain Public Address v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/blockchain-public-address-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/noDWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story.md b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..92140a70ce37f360933b6617fd0b49bdb11f10b0 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-User-Story.md @@ -0,0 +1,26 @@ +# BlockchainPublicAddress API User Stories + +| **Item** | **Details** | +| ---------- | ------------- | +| **US#1** | User Story #1 | +| ***Summary*** | As an application developer, I want a feature to fetch Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain. This way management of Blockchain Public Addresses can be perfomed by means of the phoneNumber, which is a natural concept within the OBs. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** Obtain Blockchain Public Addresses associated to a given phoneNumber of the Customer | +| ***Pre-conditions*** | N/A | +| ***Activities/Steps*** | **Starts when:** The API Consumer makes a GET request to the Blockchain Public Address API to obtain the Blockchain Public Addresses associated to a given phoneNumber (generally such addresses are identified by a DID (Decentralised Identifier, which indeed is a public address of a blockchain), composed of 26-35 alphanumeric characters in length).
                                                      **Ends when:** The API Consumer receives GET response with the list of Blockchain Public Addresses associated to the phoneNumber, including this information:
                                                      - Blockchain public address name.
                                                      - Blockchain public address identifier (DID).
                                                      - Blockchain public address identifier binding (for latter management).
                                                      - Blockchain public address currency.
                                                      Empty response will be received in case no Blockchain Public Address is linked to the phonNumber yet. | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address(es) retrieval linked to a given phoneNumber
                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      - Invalid Argument: Not valid phoneNumber.
                                                      - Internal: Server Error when fetching information. | +| -------- | ------------- | +| **US#2** | User Story #2 | +| ***Summary*** | As an application developer, I want a feature to manage (bind/unbind) Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** Manage Blockchain Public Addresses binding/unbinding them to a given phoneNumber of the Customer | +| ***Pre-conditions*** | Blockchain Public Address exists in advance | +| ***Activities/Steps*** | **BINDING PROCESS**
                                                      **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address API to bind a specific Blockchain Public Addresses to a provided phoneNumber.
                                                      **Ends when:** The API Consumer receives POST response with this unique binding identifier.

                                                      **UNBINDING PROCESS**
                                                      **Starts when:** The API Consumer makes a DELETE request to the Blockchain Public Address API to unbind a specific Blockchain Public Addresses - phoneNumber relationship, providing the binding identifier that identifies such relationship.
                                                      **Ends when:** The API Consumer receives DELETE response indicating a successful process performed (i.e. deletion). | +| ***Post-conditions*** | **BINDING PROCESS**
                                                      Binding relationship between Blockchain Public Address and phoneNumber is created. If making GET request an item showing that binding is included.

                                                      **UNBINDING PROCESS**
                                                      Binding relationship between Blockchain Public Address and phoneNumber is deleted. If making GET request the item showing that binding is no longer included. | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address management

                                                      **BINDING PROCESS**
                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      - Invalid Argument: Not valid phoneNumber and/or BlockChain Public Address Information.
                                                      - Internal: Server Error when fetching information.

                                                      **UNBINDING PROCESS**
                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      - Invalid Argument: Not valid binding identifier.
                                                      - Internal: Server Error when fetching information. | +| **US#3** | User Story #3 | +| ***Summary*** | As an application developer, I want a feature to manage bind Telco Operator customers Blockchain Public Addresses in a user-friendly way, using Customers Mobile Subscription (i.e. phoneNumber), as a natural and regular pair for the public address of a blockchain, and also performing Binding Enforcement by ensuring the phoneNumber and the blockchainPublicAddress belongs to the same owner | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** Manage Blockchain Public Addresses binding to a given phoneNumber of the Customer with Binding enforcement feature requested | +| ***Pre-conditions*** | Blockchain Public Address exists in advance | +| ***Activities/Steps*** | **BINDING PROCESS**
                                                      **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address API to bind a specific Blockchain Public Addresses to a provided phoneNumber, also indicating the nonce and signature fields.
                                                      **Ends when:** The API Consumer receives POST response with this unique binding identifier. | +| ***Post-conditions*** | **BINDING PROCESS**
                                                      Binding relationship between Blockchain Public Address and phoneNumber is created. If making GET request an item showing that binding is included. | +| ***Exceptions*** | Several exceptions might occur during the Blockchain Public Address management

                                                      **BINDING PROCESS**
                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      - Invalid Argument: Not valid phoneNumber, BlockChain Public Address, nonce or signature Information.
                                                      - Internal: Server Error when fetching information. | \ No newline at end of file diff --git a/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist.md b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..15df914c6dac9e769102808df9eab1530024edc9 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for BlockChain Public Address Validation v0.1.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address-validation.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/blockchain-public-address-validation.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/blockchain-public-address-validation-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYASD) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story.md b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..ce6d1aa0c6feed303fb6ca6739dfbbc335c13561 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/API_documentation/blockchain-public-address-validation-User-Story.md @@ -0,0 +1,11 @@ +# BlockchainPublicAddress Validation API User Stories + +| **Item** | **Details** | +| ---------- | ------------- | +| **US#1** | User Story #1 | +| ***Summary*** | As an application developer, I want a feature to generate a nonce (one-time challenge) associated to a blockchain public address, in order for the customer to be able to sign it off-chain, generating a signature. This will allow afterwards to perform binding enforment via Blockchain Public Address binding process. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** Obtain a nonce associated to a blockchainPublicAdress of the Customer | +| ***Pre-conditions*** | N/A | +| ***Activities/Steps*** | **Starts when:** The API Consumer makes a POST request to the Blockchain Public Address Validation API to obtain a nonce associated to a blockchainPublicAdress (indicated as an input) of the Customer.
                                                      **Ends when:** The API Consumer receives POST response with the nonce value. | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the nonce generation
                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      - Invalid Argument: Not valid blockchainPublicAddress.
                                                      - Internal: Server Error when fetching information. | diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06.md new file mode 100644 index 0000000000000000000000000000000000000000..88178643256bbfbbbbda3281ccd0677afa01c024 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-06.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-jul-2023
                                                      +**Status:** FINAL + + +## Attendees +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jose Antonio Ordoñez Lucena (Telefonica) +- Pedro Díez (Telefonica) + + +## Goals +WG Kick-Off Meeting
                                                      + + +Item | Who | Description +---- | ---- | ---- +Members Presentation | WG | Members Presentation +[Issue#2](https://github.com/camaraproject/BlockchainPublicAddress/issues/2) | Telefonica | Kick-Off 6th July +[Issue#3](https://github.com/camaraproject/BlockchainPublicAddress/issues/3) | Telefonica | Initial Use Cases Proposal +[PR#4](https://github.com/camaraproject/BlockchainPublicAddress/pull/4) | Telefonica | BlockChain Use Cases +[Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6) | Telefonica | Baseline Proposal +[PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Telefonica | Baseline Proposal (API YAML Code) + + +### Items Discussion + +Item | Discussion +---- | ---- +Members Presentation | Attendees from Deustche Telekom, Vodafone and Telefonica introduce themselves. +[Issue#2](https://github.com/camaraproject/BlockchainPublicAddress/issues/2) | Introduced by Telefonica. Compiles the agenda for Kick-Off meeting points:
                                                      • Meetings schedule: Agreed to have, in a bi-weekly basis, on Thursdays 13:00 - 14:00 CET/CEST
                                                      • Kind request for Maintainers and Codeowners. Explained the roles and provided more info offline. As tentative candidates we have: Klaus (VF) and Georgios (DT) for maintainers; Klaus (VF) and Krzysztof (DT) for codeowners. To be confirmed in the next days.
                                                      • Presenting initial proposal in the following item. +[Issue#3](https://github.com/camaraproject/BlockchainPublicAddress/issues/3), [PR#4](https://github.com/camaraproject/BlockchainPublicAddress/pull/4) | Presented Use Cases proposal, based on the rationale of providing some features to third parties to be able to manage Blockchains from end users via the phone numbers of the users. Features to fetch blockchain public addresses per phone number and to bind/unbind a Blockchain to/from a phone number.
                                                      • Comments raised by DT and VF that proposal is needed to be enhanced based on WG output in order to have some mentioned regarding AuthN/AuthZ and privacy considerations +[Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Going through the Baseline API definition. Explaining the endpoints:
                                                      - Endpoint to fetch blockchain public addresses linked for a given phoneNumber
                                                      - Endpoint to bind a blockchain public address to a phoneNumber
                                                      - Endpoint to unbind a blockhain public address <-> phoneNumber
                                                      Rationale/Background of the proposal in this [PR-WG#154](https://github.com/camaraproject/WorkingGroups/pull/154)

                                                      Main comments provided:
                                                      • Vodafone: Concerns about the use of DID as blockchain identifier as other standards/identifiers also could be used. Also comments about AuthN/AuthZ model for this API.

                                                      • Deutsche Telekom: Need to work in AuthN/AuthZ model for this API as well as management of User Consent. DT indicated their concern about using the phone number of the user to have such an association. Also DT provided during the meeting information about other forums where work about blockchain is being made:
                                                      - https://github.com/ChainAgnostic/CASA
                                                      - https://chainagnostic.org/
                                                      - https://chainagnostic.org/CAIPs/caip-2
                                                      - https://github.com/UCRegistry/chain-registry

                                                      • Telefonica commented that they are good comments to start and bear in mind; also regarding consents that there is a WG (Identity and Consent Management) where this kind of topics are been addressed. + + +### Next Steps +- Next Meetings:
                                                      + • 20th July - 13:00 - 14:00 CEST
                                                      + • 27th July - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20.md new file mode 100644 index 0000000000000000000000000000000000000000..9677aa67e32a963699c7075bec8a7930bb33cbfc --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-20.md @@ -0,0 +1,38 @@ +# Meeting Minutes + +## Meeting Information +**Meeting Date:** 20-jul-2023
                                                      +**Status:** FINAL + + +## Attendees +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals + +Review Members Access to WG
                                                      +Next Actions
                                                      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG | WG | Check susbcription status of members +Next Actions | WG | Actions for next meeting + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG | Commented in the meeting, in order to be able to manage maintainers and code owners for the WG. Being checked by VF members (Sebastian, Klaus). Sebastian seems to have access, Klaus is managing it. Issue will be opened when members have access to WG in order to include them as maintainers/codeowners based on their github user. +Next Actions | Commented about the following:
                                                      • Adopting github templates as per Commonalities. To be more agile, Rafał (DT) will generate PR so it can be reviewed and merged (currently only Pedro as codeowner) [PR#8](https://github.com/camaraproject/BlockchainPublicAddress/pull/8). Generated after meeting. Reviewed and Merged.

                                                      • Blockchain identification: Use of a DID is to ensure the "user identification" within a blockchain. The fact of binding it to a phoneNumber is to make a friendly way for Devs and Users to manage transactions between blockchains in a more natural way.

                                                      • Comments raised by VF in order to provide more detail in Use Cases. Deeping into access to the functionality and privacy topics. Issue to be opened by TEF in order to provide information and begin discussion (that can be lead into Use Cases description enhancements and API spec adjustments).

                                                      • Question raised by VF within [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6) about the need of indicating a currency in binding and fetch blockchain functionality. Within a given blockchain, several currencies may be used, so it might not be considered as mandatory in design. Also, Use Cases can guide in the inclusion of this metainformation. TEF will also check internally this. + + +### Next Steps + +- Next Meetings:
                                                      +• 27th July - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27.md new file mode 100644 index 0000000000000000000000000000000000000000..36f95076d7b552dc63ee0e823fbe95b52859f3b9 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-07-27.md @@ -0,0 +1,46 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 27-jul-2023
                                                      +**Status:** FINAL + + + +## Attendees + +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Georgios Papadopoulos (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
                                                      +Open Issues
                                                      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Sebastian (VF) already has access to WG. Klaus (VF) is managing it. Georgios (DT) will manage it. After that, PR will be generated to indicate maintainers and codeowners. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Telefonica provides more info about Use Cases. Vodafone comments the topic of how to manage the consent of accessing the information (GET List of Blockchains of a given phonenumber). If this endpoint can be accessed vía 2-legged how this access can be controlled in a way the user's phone owner can control the list of people they can view his blockchain addresses. Several initial options commented during the meeting (functionality to have whitelist option where indicate phonenumbers that can access blockchain of other phone numbers, hashing of blockchain and/or phone number). Need to have more discussion around the issue. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Issue opened to reflect the point raised by Vodafone regarding 'currency' as mandatory parameter. Vodafone indicates there are many use cases (e.g. smart contract tokens) where transactions within the same blockchain can be performed with different currencies. Deutsche Telekom also agrees on that. Telefonica needs to check internally (mentioned that initial proposal was to consider one currency but open to cover also other scenarios). TEF will provide feedback and proposal about this topic. +AoB | Control of rate limit of requests, commented by Deustche Telekom. To have some rate control policy in Telco Operator API GW, needed to cover it in API design. There is some exception defined in commonalities: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md#32-http-response-codes (HTTP 429). Agreed to include within API design. AP@Pedro to include in API Proposal + +### Next Steps + +- Next Meetings:
                                                      +• 10th August - 13:00 - 14:00 CEST
                                                      +• 31th August - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10.md new file mode 100644 index 0000000000000000000000000000000000000000..4ac8bd70edb29e02f70e830c0467b1d9ca59324f --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-10.md @@ -0,0 +1,49 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 10-ago-2023
                                                      +**Status:** FINAL + + + +## Attendees + +- Sebastian Köller (Vodafone) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
                                                      +Open Issues
                                                      + + +Item | Who | Description +---- | ---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +Consent management in API | WG | Discussion about consent Management +Baseline API Proposal | TEF | Ongoing API v0.1 + + +### Items Discussion + +Item | Discussion +---- | ---- +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Sebastian (VF) and Georgios (DT) are fully operative. Klaus (VF) and Krzysztof (DT) are managing its access. PRs triggered to update [Maintaners](https://github.com/camaraproject/BlockchainPublicAddress/pull/14) and CodeOwners (pending) accordingly. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Telefonica provides more info about Use Cases. Vodafone comments the topic of how to manage the consent of accessing the information (GET List of Blockchains of a given phonenumber). If this endpoint can be accessed vía 2-legged how this access can be controlled in a way the user's phone owner can control the list of people they can view his blockchain addresses. Several initial options commented during the meeting (functionality to have whitelist option where indicate phonenumbers that can access blockchain of other phone numbers, hashing of blockchain and/or phone number). Need to have more discussion around the issue. New [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) created +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Proposal presented by Telefonica in order to address this comment. VF(Sebastian) seems OK to this proposal. Georgios (DT) would like to check offline, to identify whether can be 'scam' scenarios that may need currency. +Enhancement due to consent management | Explain the context of consent management within API. After meeting new [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) opened, summarizing info. Main topic concern raised here are (DT, VF) the following:
                                                      • Whether this consent is "forever" or "one time use". Once User B gives consent, anyone could access to such info.
                                                      • Whether this consent has to be more fine-grained, so as provided only for the User A access (i.e. have granularity to be settled per user phoneNumber level).

                                                      TEF asks whether according to these comments it is being thinking in an UX where User B is prompted with a screen to give their consent for any API call for any User A's request, and response is yes. TEF will also check internally about its product view on that. Related to this, Rafał indicates that this has relationship with Identity&ConsentManagement WG and regarding picture provided just not to include (at least) within CAMARA API spec as it includes conventions outside CAMARA. It will be taken out and in future check if makes sense to add something GSMA OpenGateway agnostic. +AoB | Control of rate limit of requests, commented by Deustche Telekom. To have some rate control policy in Telco Operator API GW, needed to cover it in API design. Exception 429 already considered into the proposal. +Baseline API Proposal [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5)| Points performed:
                                                      • Renamed OB to Telco Operator
                                                      • Adding Exception 429
                                                      • Removed Image.
                                                      Pending Points:
                                                      • `currency` topic
                                                      • Impacts in API derived from Consent Management + + +### Next Steps + +- Next Meetings:
                                                      +• 31th August - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31.md new file mode 100644 index 0000000000000000000000000000000000000000..2b27fc4b601e6a66d2baa28df3676eb708de967c --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-08-31.md @@ -0,0 +1,51 @@ +# Meeting Minutes + +## Meeting Information + +**Meeting Date:** 31-ago-2023
                                                      +**Status:** FINAL + + + +## Attendees + +- Stefan Engelbert (Aloaha) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Rafał Artych (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + + +## Goals + +Review Members Access to WG
                                                      +Next Actions
                                                      + + +Item | Who | Description +---- | ---- | ---- +MOM-2023-08-10 - [PR#17](https://github.com/camaraproject/BlockchainPublicAddress/pull/17) | WG | MOM-2023-08-10 +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +Baseline Proposal [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | TEF | Basline API Proposal +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management + + +### Items Discussion + +Item | Discussion +---- | ---- +Welcome to new members | Stefan Engelbert (Aloaha) joins the WG. +MOM-2023-08-10 - [PR#17](https://github.com/camaraproject/BlockchainPublicAddress/pull/17) | Pending Approval, reviewed by Georgios and Sebastian. Will ask Jose Antonio Lucena (TEF) in the meantime other codeowners are added to approve them, so it can be merged. CODEOWNERS and Maintainers files cannot be updated until involved people has WG access. Also Krzysztof will trigger PR to include as a codeowner so Pedro can approve it and therefore have codeowners in the short-term from two companies at least. +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | No news about Klaus status. Asked him offline. Check again next week. +Baseline Proposal [Issue#6](https://github.com/camaraproject/BlockchainPublicAddress/issues/6), [PR#5](https://github.com/camaraproject/BlockchainPublicAddress/pull/5) | Pedro comments TEF has intention to perform an MVP based on initial proposal and asks WG if we can merge it in order to be able to indicate CAMARA compliance. This does not enter in contradiction with the fact that API can and will be evolved based on output of discussions and future requirements. This version will be set as "v0.1". Also we will have a reference to evolve from it. It is understood within the WG and it is OK to move forward and merge. Pedro will check and make some refinements and advise for review. Intention is to merge (if possible) during 4th September week. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Georgios comments it will be needed more time to have a view about currency relationship with the Public Address. Then this issue will be KEPT OPEN. Also comments from Stefan, Krzysztof (topic of having some model to signal/identify chain_id), mentioning [https://chainagnostic.org/CAIPs/caip-2](https://chainagnostic.org/CAIPs/caip-2) (this reference was also provided during July) and Sebastian about potential anidated blockchain "type" model. Summary gathered within then issue and participants will comment over this. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro comments that this topic has raised internally but no feedback yet due to holidays period. In two directions:
                                                      • About product perspective to manage consent in every GET access to the blockchain information of a given user
                                                      • In the way of "having" API functionality to manage some kind of whitelists to "allow trusted contacts" the access without request consent. +AoB | Next Meetings, next meeting scheduled for 28th September. Pedro is on holidays next weeks and comments to the WG if any meeting would like to be managed in the meantime, 14th September could be an option (up to WG in case other members consider suitable) + +### Next Steps + +- Next Meetings:
                                                      +• 28th September - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28.md new file mode 100644 index 0000000000000000000000000000000000000000..2355c5d7965c2a7499ec103468d6e21743398806 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-09-28.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-sep-2023
                                                      +**Status:** FINAL + +## Attendees + +- Stefan Engelbert (Aloaha/CodeB) +- Rafał Artych (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Currently, initial baseline version (v0.1) is generated. A tag will be generated to track this baseline version (PR to be generated). Next steps are to progress in open issues and after that review Use Stories description. After meeting, Pedro (TEF) synchronized status with Krzysztof (DT) that joined later. Also bi-weekly meetings will be scheduled. +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | Klaus (VF) and Krzysztof (DT) pending to enable their subscription to the WG. Sebastian (VF) will comment internally to Klaus and Pedro (TEF) comments offline to Krzysztof. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Pending comments by Georgios, issue is kept OPEN and to be reviewed in next meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro comments it will be reviewed internally with Product next week in order to have feedback. Initially, Use Case addressed by TEF is to set up consent once per user. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Sebastian (VF) explains rationale for this topic. Underlying idea is to have a (reduced) set of manually defined layer 1 blockchains and optionally use the chainId for layer 2 blockchains or testnets within that ecosystem. For instance for EVM-based chains, there is an already defined chainId for them in https://chainlist.org/. Stefan (CodeB) agrees with this proposal baseline. Pedro (TEF) will check in detail. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 5th October - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05.md new file mode 100644 index 0000000000000000000000000000000000000000..a1c1a6867a0905e1bd72231fa2febf42d1dbba58 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-05.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 05-oct-2023
                                                      +**Status:** FINAL + +## Attendees + +- Stefan Engelbert (Aloaha/CodeB) +- Rene Reinsberg (Celo Foundation) +- Kevin Tharayil (Celo Foundation) +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | WG | Main WG participants have subscription enabled +[Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | TEF | Required 'currency' information in API design +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | New members from Celo Foundation joined the meeting (Rene, Kevin). They refer during the meeting to some initiatives they have been involved: [Minipay](https://www.opera.com/de/products/minipay) and [Valora](https://valoraapp.com/)

                                                      With regards to WG status, next step is to generate a release for the initial version v0.1.0, [PR#23](https://github.com/camaraproject/BlockchainPublicAddress/pull/23) to generate `CHANGELOG.md` is ready and will be merged after meeting.
                                                      Work done after the meeting.
                                                      • New Release tag [v0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/v0.1.0) generated.
                                                      • Release content [release-0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/tree/release-0.1.0) +Review Members Access to WG - [Issue#10](https://github.com/camaraproject/BlockchainPublicAddress/issues/10) | To make more agile WG work, Georgios (DT) and Sebastian (VF) are settled as both maintainers [PR#14](https://github.com/camaraproject/BlockchainPublicAddress/pull/14) and codeowners [PR#24](https://github.com/camaraproject/BlockchainPublicAddress/pull/24). When Klaus (VF) and Krzysztof (DT) enable their subscription we will comment to include as maintainers and codeowners. Both PRs are `MERGED` and the Issue is `CLOSED`. +Required 'currency' information in API design - [Issue#12](https://github.com/camaraproject/BlockchainPublicAddress/issues/12) | Agreed to be closed. `CLOSED` after the meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Pedro (TEF) illustrates the topic for anyone to have some background and also indicates have internally address this with their product team and their concern is that the checking for the permission for every transaction may be a stopper for business cases as it is not the best performance, also indicates that probably some product guidance from GSMA OGW would be helpful. Sebastian indicates that it should be avoided that personal information can be leaked by anyone and we should ensure the restricted access to this information. Georgios also comments not only the access to blockchain info but the knowledge of phone numbers that can be used for spaming services. In this context, Celo comments about some work they have performed in [user identity in blockchain](https://docs.celo.org/protocol/identity/odis-use-case-phone-number-privacy). +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Rationale of the proposal explained by Sebastian is understood. Georgios comments the proposal is in line with the objective of a better blockchain identification scheme. Pedro also comments it is a good way forward and asks some clarification questions, about the identification of ethereum mainnet in this model (blockchain=evm, chainId=1) and to check this proposal does not enter in contradiction with the use of DID for the identification of the blockchain address, where Sebastian indicates there is no constrain/restriction. Pedro will draft a proposal within the issue to get a consensus on this. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 19th October - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19.md new file mode 100644 index 0000000000000000000000000000000000000000..a235813b79abce358b141fab22dd2cd0c0968e47 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-10-19.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 19-oct-2023
                                                      +**Status:** FINAL + + +## Attendees + +- Kevin Tharayil (Celo Foundation) +- Rafał Artych (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Klaus Reifenrath (Vodafone) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +WG Kick-Off Meeting
                                                      + + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | WG current status +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Two topics commented:
                                                      • WG repository information after release generation and merging of [PR#25](https://github.com/camaraproject/BlockchainPublicAddress/pull/25). New release is available [Release v0.1.0](https://github.com/camaraproject/BlockchainPublicAddress/releases/tag/v0.1.0) and [CHANGELOG.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/CHANGELOG.md) and [README.md](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/README.md) are updated.
                                                      • Manage members subscription: Klaus and Krzysztof will re-trigger the WG subscription request so as they will enable their subscription and link their github user. Later on, it will be possible to manage them as maintainers/codeowners. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Sebastian presented a proposal in order to manage every type of blockchain. Relying in one parameter to identify L1 Ecoystems and other one for identifying L2 and subsequent levels. Pedro and George seems initially OK. Latest comment of using `ethereum` instead of `evm` was in line to indicate real L1 ecosystems within 'blockchain' field, so the reason to also indicate other ecosystems like Avalanch even they have a chainId in evm naming format. This was explained in the meeting as asked by Krzysztof as a doubt. Krzysztof also mentioned whether the list of supported chainIds has to be restricted, Klaus comments that should be left open (initially no restriction in API input); Pedro indicates that in principle API design can support all and to deal with those business scenarios where a given chainId is not supported (a user wallt that does not manage specific blockchains) an exception may be defined. There is more discussion around this topic ( Krzysztof refers to CAIP - https://chainagnostic.org/CAIPs/caip-2, Klaus also mention to other scheme https://eips.ethereum.org/EIPS/eip-3220), in order to have a flexible way to identify a huge amount of blockchain ecosystems. There is certainty about evm chainId (https://chainid.network/, https://chainid.network/chains.json) is unique for evm based chains. After some discussion, Klaus comment the idea of having the identification in a common parameter (name to be decided, WG thinks offline) and that parameter indicates the L1-"sub-id" in a flexible way. It seems a way forward and WG will think about a name. In the meantime Pedro will trigger WIP PR to begin to detail this proposal and also improve/evolve with comments received. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF (Pedro) explains this topic can be resumed in order to improve/enhance description of Use Cases with the context discussed these months. Also provides information about Use Cases TEF business is thinking about. To be checked offline and provide feedback by WG members. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Not covered during this meeting. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 2nd November - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02.md new file mode 100644 index 0000000000000000000000000000000000000000..53aee44c38831d74490278a34ff3332fd76fa9b1 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-02.md @@ -0,0 +1,41 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 02-nov-2023
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +[PR#29](https://github.com/camaraproject/BlockchainPublicAddress/pull/29) | WG | Create MOM-2023-10-19 +[PR#31](https://github.com/camaraproject/BlockchainPublicAddress/pull/31) | DT | Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +Create MOM-2023-10-19 - [PR#29](https://github.com/camaraproject/BlockchainPublicAddress/pull/29) | Meeting Minutes of 19th October Meeting ready for review. Commented during the meeting the review of them to have the approval and merge them. +Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository - [PR#31](https://github.com/camaraproject/BlockchainPublicAddress/pull/31) | PR triggered by DT (Rafał) in order to align WG repository with the guidelines of CAMARA regarding [Testing Folder](https://github.com/camaraproject/Template_Lead_Repository/pull/1). Reviewed and approved. `MERGED` after the meeting +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | As commented during last meeting, Pedro triggered a PR to compile the output of the Issue. The proposal is under [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30), along with other Commonalities alignments and editorial enhancements. The target name of the parameter to identify the blockchain is still TBD (currently appears as `blockchain`). Pedro (TEF) indicates it is still pending to add the exception to manage the scenario mentioned by Krzysztof (DT) in the last meeting, but generated in advance to receive comments from the participants. Georgios (DT) gave an OK to the proposal in terms of the description provided. Krzysztof (DT) and Sebastian (VF) will review offline. Sebastian also asks two points:
                                                      • If Issue#19 will be closed after the merging of this PR, and Pedro indicates that this is the objective (keeping v0.2.0-wip, just to discuss later within the WG the next steps).
                                                      • The meaning of `` within the blockchain identification model, where Pedro answers it is the name given to the concept under L2 and Testnets blockchain identification (in EVM it matches the concept of chainId), and it is open to receive inputs if other name is considered more suitable, and for sure it can be reviewed in the future. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Commented during the meeting to check this issue by participants in order to receive comments and see if further description is incorporated into Use cases description document. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF indicates next week will synchronize this point internally with Business and comment back to the issue. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 16th November - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16.md new file mode 100644 index 0000000000000000000000000000000000000000..39385321baf5fa12d0ebd9141f84ce6322b4341a --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-16.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 16-nov-2023
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jorge Ordovas (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | TEF | Deep Into Use Cases +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Today joins meeting Jorge Ordovas (TEF, Business Unit Web3 proyects). Currently main focus within WG is an aligment in Blockchain Identification Model. Meeting Minutes from [19/OCT](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/documentation/MeetingMinutes/MOM-2023-10-19.md) and [02/NOV](https://github.com/camaraproject/BlockchainPublicAddress/blob/main/documentation/MeetingMinutes/MOM-2023-11-02.md) are available. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | Proposal is under [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30), some wording comments provided by Rafał (DT), already fixed. Also he refers to Commonalities Issues [camaraproject/Commonalities#77](https://github.com/camaraproject/Commonalities/issues/77) and [camaraproject/Commonalities#80](https://github.com/camaraproject/Commonalities/issues/80), which are noted to be addressed in this PR or a future one, based on their respective output.
                                                      Some background context is provided for Jorge (TEF) also understands the rationale of this track.
                                                      Pending point is to agree on a field name for this concept, some suggestions provided by Pedro (TEF) within the Issue. Georgios (DT) indicates his preference is `blockchainNetworkId` and also asks whether makes sense to have some alignment in the wording for the BlockChainPublicAddress. Pedro (TEF) comments doesn't think so as this field is to indicate which Blockchain Network the BlockchainPublicAddress belongs to. Some days will be given to provide preferences among participants and selected name will be updated within PR, so as setting for final review. +Deep Into Use Cases - [Issue#11](https://github.com/camaraproject/BlockchainPublicAddress/issues/11) | Will be closed during this week if no further comment provided. It can be also discussed in the future. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Feedback from TEF. Business Unit is performing Privacy Assesment about this funcionality, therefore will be kept On-Hold until having their input about this. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 30th November - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30.md new file mode 100644 index 0000000000000000000000000000000000000000..ad91b5269b8840cc3b696e6d90899eba88a442fd --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-11-30.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 30-nov-2023
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Sebastian Köller (Vodafone) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | VF | Solving the chain identification issue +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | After [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) merge, v0.2.0-wip is available in code folder. So far, it will be kept `ON-HOLD`, until some Commonalities guidance are being resolved (i.e. AuthN/AuthZ section), so it can take advantage before generating a new release if required. +Solving the chain identification issue - [Issue#19](https://github.com/camaraproject/BlockchainPublicAddress/issues/19) | `CLOSED` after review and approval of [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) by Georgios (DT) and Sebastian (VF) respectively. [PR#30](https://github.com/camaraproject/BlockchainPublicAddress/pull/30) is `MERGED` during the meeting. +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Feedback from Pedro (TEF). Business Unit Privacy Assesment is still pending and probably will happen next year. Will be kept `ON-HOLD` until it. +AoB | Some topics during the meeting:
                                                      • Georgios (DT) asks whether implementation topics are discussed within CAMARA WG scope. Pedro (TEF) comments implementation is not under the scope of CAMARA but probably hosted in the context of Operators meetings within each country, where alignment about implementation of different APIs/features is taking place (a.k.a. local champions).
                                                      • Pedro (TEF) indicates it will trigger a new PR to add Krzysztof as codeowner.
                                                      • Sebastian (VF) shares with the WG he will be leaving it by the end of this year. WG appreciates the effort and contribution from Sebastian during these months. A PR will be triggered to removed him as a maintainer and codeowner.
                                                      • Agreed to have next meeting on 12th December (same slot), being the latest during this year. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 12th December - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12.md new file mode 100644 index 0000000000000000000000000000000000000000..39606cccbae636a709fb89b4d7aa8c3aea381803 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2023-12-12.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 12-dec-2023
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Jorge Ordovas (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +Maintainers and Codeowners | WG | Update Maintainers and Codeowners +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | API specification v0.2.0-wip is available in code folder. Kept `ON-HOLD`, until some Commonalities guidance are being resolved (i.e. AuthN/AuthZ section), so it can take advantage before generating a new release if required. To be reviewed next year. +Maintainers and Codeowners | Update of maintainers and codeowners:
                                                      • Maintainers - [PR#35](https://github.com/camaraproject/BlockchainPublicAddress/pull/35) `MERGED`: Removed Jose Antonio (TEF) and Sebastian (VF).
                                                      • Codeowners - [PR#36](https://github.com/camaraproject/BlockchainPublicAddress/pull/36) `MERGED`: Removed Jose Antonio (TEF) and Sebastian (VF). Added Krzysztof (DT). +API Enhancement due to Consent Management - [Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Kept `ON-HOLD` until next year. +AoB | Some topics during the meeting:
                                                      • Pedro (TEF) will ping offline Klaus (VF) to check whether is going to participate within the WG next year as Sebastian has leaved the WG.
                                                      • Pedro (TEF) comments WG about existance of slack channel that may help to be more agile in tech discussions. [Link](https://join.slack.com/t/camara-project/shared_invite/zt-23bjzwes5-4aLBtE_E1sO0BJhCLBdZVQ).
                                                      • Rafał (DT) comments about traversal work regarding CAMARA linting rules. Main contributions are [Commonalities/PR#74](https://github.com/camaraproject/Commonalities/pull/74) and [Commonalities/PR#110](https://github.com/camaraproject/Commonalities/pull/110). Ask for volunteers to apply in Blockchain (Pedro offers as volunteer, will open an issue to track it). Krzysztof (DT) asks about the WoW and Rafał comments the initial intention is to test these linting rules in every CAMARA WG to check its behaviour and make refinements if any. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 11th January - 13:00 - 14:00 CEST
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25.md new file mode 100644 index 0000000000000000000000000000000000000000..a89608198e063aa9d685002e0aa205923047eeb2 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-01-25.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-jan-2024
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Jorge Ordovás (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | WG | Linting rule set for Blockchain Public Address API +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | The meeting was a brief update on some administrative and technical topics of the blockchain working group. The main points discussed were:
                                                      • Asked Georgios as codeowner to review and approve the minutes of the last meeting.
                                                      • Pedro said that he will be contacting Klaus to know if he is planning to attend again the working group.
                                                      • Pedro proposed to have meetings based on demand and to use the blockchain slack channel to communicate the topics of the next meetings. Georgios and Rafał agreed with Pedro's approach.
                                                      • Pedro suggested to keep the current evolution of the justification until the discussions on the blockchain identification and the commonalities were resolved. +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Still `ON-HOLD` waiting for the business feedback on a privacy evaluation/assesment. +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | Pedro shared that he already applied the linter in a fork. Thanks to Rafał support and guidelines to enable this. A thread will be opened in the Issue#38 to comment on the results and the necessary particularizations for blockchain. Rafał added that the linter rules might need some changes or updates comming from Commonalities track. +AoB | Next pending points are:
                                                      • Review the output of the linter and make the necessary adjustments in the API specification.
                                                      • Follow the thread of the Issue#38 and provide comments or suggestions.
                                                      • Consult with the business team if there was any new requirement or prioritization for the new year.
                                                      • Be attentive to the business feedback on the issue #16 and decide how to proceed.
                                                      • Join the slack channel of blockchain for participants and be aware of the calls for the next meetings. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: TBD, on demand
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22.md new file mode 100644 index 0000000000000000000000000000000000000000..b377169d5524f4d814d38407ad8f289231358b53 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-02-22.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-feb-2024
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Georgios Papadopoulos (Deutsche Telekom) +- Krzysztof Sielski (Deutsche Telekom) +- Jorge Ordovás (Telefónica) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | WG | Linting rule set for Blockchain Public Address API +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | **Linter Rules**: The linter rules from commonalities have been tested successfully and will be applied to the working group repository. New Issue and related PR will be triggered in the next weeks. AP@Pedro
                                                      **New Topic**: An issue will be created to discuss how to handle the scenario of requesting a binding for a configuration that already exists. The proposed solution is to use the 409 conflict error code. AP@Pedro +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | The issue of consent management and privacy will be resumed in the next meeting, as there is no clear business feedback yet. Pedro wants to have some guidelines or conclusions to move forward with this topic. Agreed by Jorge, Georgios, Krzysztof, Rafał. +[Issue#38](https://github.com/camaraproject/BlockchainPublicAddress/issues/38) | Linter tested OK, then issue is `CLOSED`. +AoB | Pedro contacted Klaus (VF) offline and informed that Klaus will not join the working group for the time being (short-term). Maybe in the mid-term. He will follow offline the progress.
                                                      Next meetings (next two months due to Pedro personal matter) will be moved temporarily to 11:00 - 12:00 CET Time. Agreed by the team. NOTE: Changed after the meeting to 11:30 - 12:30 for Jorge to be able to attend.

                                                      Pending points for the next meeting are:
                                                      • Discuss the issue of consent management and privacy and try to reach a conclusion or a way-forward.
                                                      • Review the issue and the pull request for the 409 conflict error code scenario. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 7th March, 11:30 - 12:30 CET
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07.md b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07.md new file mode 100644 index 0000000000000000000000000000000000000000..7fcb9ec0d4a9130212a11423e3690784819255b2 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/MOM-2024-03-07.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-mar-2024
                                                      +**Status:** FINAL + + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefónica) + + +## Goals +Review of Issues/PRs and next steps
                                                      + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | BlockchainPublicAddress WG Status +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | TEF, WG | API Enhancement due to Consent Management +[Issue#46](https://github.com/camaraproject/BlockchainPublicAddress/issues/46) | TEF | Manage Duplicated Bindings and Improve Description +AoB | WG | Other topics + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | **Linter Rules**: Linter rules applied and working successfully. Thanks to all support from Rafał.
                                                      **Meeting Minutes 22th/February**: [Minutes](https://github.com/camaraproject/BlockchainPublicAddress/pull/43) approved and `MERGED`. +[Issue#16](https://github.com/camaraproject/BlockchainPublicAddress/issues/16) | Georgios, Rafal and Jorge cannot attend the meeting. The issue is postponed until the next meeting. +[Issue#46](https://github.com/camaraproject/BlockchainPublicAddress/issues/46) | Manage Duplicated Bindings and Improve Description. Issue opened by Telefonica, to address the case when a binding with a specific configuration (phoneNumber, blockchainNetworkId, blockchainPublicAddress and optionally currency) already exists, and a new one (POST) with the same configuration is triggered. The proposed exception is `HTTP 409 - CONFLICT`. Also some description rewording and fixing is proposed. Commented during the meeting to be reviewed offline and talk in the next meeting. Generated related [PR#47](https://github.com/camaraproject/BlockchainPublicAddress/pull/47). +AoB | Pedro indicates he is not able to attend next meeting (21th March). Rafał also cannot. Then the next meeting will be held on 4th April. + + +### Next Steps +- Next Meetings:
                                                      + • Next meeting: 4th April, 11:30 - 12:30 CET
                                                      diff --git a/original/BlockchainPublicAddress/documentation/MeetingMinutes/README.MD b/original/BlockchainPublicAddress/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..084ad18a09ef61b7037c1560fc0585dfe99292dd --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/MeetingMinutes/README.MD @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since 4th April WG Meeting, meeting minutes are placed in [CAMARA Blockchain Public Address WG Wiki Confluence site](https://lf-camaraproject.atlassian.net/wiki/x/thDe) \ No newline at end of file diff --git a/original/BlockchainPublicAddress/documentation/SupportingDocuments/README.MD b/original/BlockchainPublicAddress/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/BlockchainPublicAddress/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/CallForwardingSignal/README.md b/original/CallForwardingSignal/README.md new file mode 100644 index 0000000000000000000000000000000000000000..27722b1e5458f12ef9d568f051ebf30aee2bb4c7 --- /dev/null +++ b/original/CallForwardingSignal/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# CallForwardingSignal + +Incubating API Repository to evolve and maintain the definitions and documentation of CallForwardingSignal Service API within the Sub Project [Call Forwarding Signal](https://lf-camaraproject.atlassian.net/wiki/x/IIAfBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/HADe) + +## Scope +* Service APIs for “CallForwardingSignal” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * retrieve information about the status of the Call Forwarding Service on a specific phone number. + * avoid fraud leveraging the Call Forwarding Service. + * The main scope of the Call Forwarding Signal API is anti fraud to avoid fraudsters to use the Call Forwarding Service to carry on a scam. Other use cases are anyway supported by the Call Forwarding Signal API that also provides additional endpoints to detect the general Call Forwarding Service settings. +* Describe, develop, document and test the API +* Started: February 2024 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.3](https://github.com/camaraproject/CallForwardingSignal/releases/tag/r3.3) (Fall25), with the following API versions: + * **call-forwarding-signal v0.4.0** + [[YAML]](https://github.com/camaraproject/CallForwardingSignal/blob/r3.3/code/API_definitions/call-forwarding-signal.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CallForwardingSignal/r3.3/code/API_definitions/call-forwarding-signal.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CallForwardingSignal/r3.3/code/API_definitions/call-forwarding-signal.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CallForwardingSignal/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CallForwardingSignal/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CallForwardingSignal/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Monday 15h-16 CET, usually every two weeks. For the next meetings information, have a look on the [API Wiki Page](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14549020/CallForwardingSignal). + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96706226837?password=2d113354-bf97-4441-8d6d-9fd0ae69f2d1) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14574452/CallForwardingSignal+Minutes?atlOrigin=eyJpIjoiNjc1Mzc3ZWIwNGI4NGRhMmE2YjBkMGFjNmFjMTNiZDUiLCJwIjoiYyJ9) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to all Contributors of this Sub Project can be sent using . diff --git a/original/CallForwardingSignal/code/API_definitions/call-forwarding-signal.yaml b/original/CallForwardingSignal/code/API_definitions/call-forwarding-signal.yaml new file mode 100644 index 0000000000000000000000000000000000000000..2cac43ce39c73718c9297a8144516bd68a5e119b --- /dev/null +++ b/original/CallForwardingSignal/code/API_definitions/call-forwarding-signal.yaml @@ -0,0 +1,599 @@ +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Call Forwarding Signal + description: | + # Overview + The Call Forwarding Signal API provides the API Consumer with + information about the status of the Call Forwarding Service on a specific + phone number. The main scope of the Call Forwarding Signal API is "anti + Fraud" to avoid fraudsters to use the Call Forwarding Service to carry + on a scam. Other use cases are anyway supported by the Call Forwarding + Signal API that also + provides additional endpoints to detect the general Call Forwarding + Service settings. + # Introduction + The Call Forwarding Service is provided by the Network to a phone + number. This service redirects the incoming call to that phone number + to an alternative destination such as another phone number or a voice mail + system. There are two main types of call forwarding settings: + unconditional and conditional. + The Call Forwarding Signal API can be invoked to detect if the unconditional + call forwarding service is active. The Call Forwarding Signal API can also + be invoked to + get the general status of the Call Forwarding Service (inactive, + conditional, unconditional). If conditional call forwarding is active, + the different type of settings are returned ('conditional_busy', + 'conditional_not_reachable', 'conditional_no_answer'). + + **Example use cases:** + + [**Bank Frauds**](https://github.com/camaraproject/CallForwardingSignal/discussions/3#discussioncomment-8694420) + + [**Alert Interception**](https://github.com/camaraproject/CallForwardingSignal/discussions/3#discussioncomment-8701847) + + [**Call Forwarding Verification**](https://github.com/camaraproject/CallForwarding\Signal/discussions/3#discussioncomment-8915595) + # Quick Start + The Call Forwarding Signal API is a REST API based on the + CreateCallForwardingSignal resource. + This resource can be used, by the API Consumer, to specify the phone number + on which the Call Forwarding Service status must be verified, in case of + two-legged authentication. If three-legged authentication is used the phone + number is instead detected, by the API Producer, from the access token. + + Before starting to use the Call Forwarding API, the developer needs to know + about the below specified details: + + **phoneNumber** + This is the end user phone number. The Call Forwarding Signal API verifies + if a call forwarding + service is active on this phone number. Note: this parameter must be + must be provided/valued only in case of two-legged authentication. + In case of three-legged authentication the phone number is retrieved by + the access token. + + **CreateCallForwardingSignal** + This is the resource the API Consumer uses to define the phone number to + be verified about the status of the Network Call Forwarding service. + + **UnconditionalCallForwardingSignal** + This is the resource the API Consumer gets back, containing the information + about the Unconditional Call Forwarding Service status for the given phone + number (PhoneNumber). + + **CallForwardingSignal** + This is the resource the API Consumer gets back, containing the information + about the general status of the Network Call Forwarding service for the + specified phone number. + + The Call Forwarding Signal API provides two endpoints fulfilling the + following intents: + - **unconditional-call-forwardings**: Is the unconditional call fwd service + active on a specific phone number? + - **call-forwardings**: Which is the status of the call forwarding for a + specific phone number? + # API Documentation + ## Details + The Call Forwarding Signal API is invoked by an API Consumer after the + Consent Management flow. + + The API Consumer can request the API Producer for the status of the + Unconditional Call Forwarding service using the + unconditional-call-forwardings POST method. A boolean, with the information + about the activation status of the call forwarding service, will be + provided back via the UnconditionalCallForwardingSignal resource. + + The API Consumer can also request the API Producer for the generic status of + the Call Forwarding service using the call-forwardings POST method. An array + of strings with the information of the type of active call forwarding + services will be provided back via the CallForwardingSignal resource. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Identifying the phone number from the access token + This API requires the API consumer to identify a phone number as the + subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject + will be identified from the optional `phoneNumber` object field, which + therefore MUST be provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a + three-legged access token to invoke the API by relying on the + information that is associated with the access token and was + identified during the authentication process. + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `phoneNumber` object field is not included in the request, then + the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the + optional `phoneNumber` object field is also included in the request, then + the server will return an error with the `422 UNNECESSARY_IDENTIFIER` + error code. This will be the case even if the same device is + identified by these two methods, as the server is unable to make + this comparison. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + # FAQ's + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/CallForwardingSignal +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/call-forwarding-signal/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +############################################################################ +# Tags # +############################################################################ +tags: + - name: Unconditional Call Forwarding information retrieval + description: Provides information on Unconditional Call Forwarding + settings for the provided phone number (PhoneNumber) + - name: Call Forwarding information retrieval + description: Provides information on Call Forwarding settings for the + provided phone number (PhoneNumber). +############################################################################ +# Paths # +############################################################################ +paths: + /unconditional-call-forwardings: + post: + tags: + - Unconditional Call Forwarding information retrieval + security: + - openId: + - 'call-forwarding-signal:unconditional-call-forwardings:read' + summary: Retrieve the information about the status of the + unconditional call forwarding service on a phone number (PhoneNumber) + description: This endpoint provides information about the status + of the unconditional call forwarding, being active or not. + operationId: retrieveUnconditionalCallForwarding + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallForwardingSignal' + required: true + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/UnconditionalCallForwardingSignal' + "400": + $ref: "#/components/responses/Generic400" + '404': + $ref: '#/components/responses/Generic404' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /call-forwardings: + post: + tags: + - Call Forwarding information retrieval + security: + - openId: + - 'call-forwarding-signal:call-forwardings:read' + summary: Retrieve the information about the type of call forwarding + service active on a phone number (PhoneNumber) + description: This endpoint provides information about which type of + call forwarding service is active. More than one service can be + active, e.g. conditional and unconditional. This endpoint exceeds + the main scope of the Call Forwarding Signal API, for this reason + an error code 501 can be returned. + operationId: retrieveCallForwarding + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallForwardingSignal' + required: true + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/CallForwardingSignal' + "400": + $ref: "#/components/responses/Generic400" + '404': + $ref: '#/components/responses/Generic404' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "501": + $ref: "#/components/responses/Generic501" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + description: to support Consent Management + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ############################################################################ + # Resources # + ############################################################################ + schemas: + UnconditionalCallForwardingSignal: + description: resource containing the information about the Unconditional + Call Forwarding Service for the given phone number (PhoneNumber) + type: object + properties: + active: + type: boolean + description: Indicates if the unconditional call forwarding service + is active. + CallForwardingSignal: + description: resource containing the list of the Call + Forwarding Services active for the given phone number (PhoneNumber). The + possible states are, 'inactive' (no call forwarding service activated), + 'unconditional' (call forwarded independently from the device status), + 'conditional_busy' (call forwarded if the device is on an active call), + 'conditional_not_reachable' (call forwarded if the device is not + reachable), 'conditional_no_answer' (call forwarded if the device doesn't + answer the incoming call). + type: array + items: + type: string + enum: + - 'inactive' + - 'unconditional' + - 'conditional_busy' + - 'conditional_not_reachable' + - 'conditional_no_answer' + example: + - 'unconditional' + - 'conditional_busy' + - 'conditional_no_answer' + minItems: 1 + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Request # + ############################################################################ + CreateCallForwardingSignal: + description: resource containing the phone number (PhoneNumber) regarding + which the Call Forwarding Service must be checked. To be provided/valued + only in case of two-legged authentication. If provided/valued with + three-legged authentication a 422-UNNECESSARY_IDENTIFIER error code is + returned. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + ############################################################################ + # Types # + ############################################################################ + PhoneNumber: + description: A public identifier addressing a telephone subscription. + In mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to E.164 + standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + ############################################################################ + # Responces # + ############################################################################ + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Call forwarding check can't be done because the + phone number is unknown. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the + request and the device or phone number identification + cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when + a device or phone number has already been identified + from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the + access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code + should be avoided as far as possible to get the objective + to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. diff --git a/original/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1.md b/original/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1.md new file mode 100644 index 0000000000000000000000000000000000000000..a179379930a1b0d6454d975a0e9300a7568c7ab4 --- /dev/null +++ b/original/CallForwardingSignal/documentation/API_documentation/Call-Forwarding-Signal-UserStory-UseCase-1.md @@ -0,0 +1,15 @@ + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Banks offer the option for end users to receive telephone calls to solve problems, e.g. in case of issues with the bank App, issues with Smartphones, the bank website or any tool providing access to the online bank account management system. How does the fraudster operate?
                                                      • Through social engineering, the fraudster gathers information about bank end users who are engaged in such a situation, needing the bank to contact them.
                                                      • Once they identify the service provider and the phone number of an end user, they manage to successfully activate, on the end user's profile, the 'unconditional call forwarding' to a phone number they control.
                                                      • After successfully setting up 'unconditional call forwarding,' the fraudster then contacts the bank, claiming an inability to access online banking services and requesting a call from a bank representative.
                                                      • When the bank calls the registered contact number of the end user, the active 'unconditional call forwarding' diverts the call directly to the fraudster, thus completing their scheme.
                                                      The Bank Application, before contacting the end user's phone number, invokes the Call Forwarding Signal API to verify if a "unconditional call forwarding" option is active on the end user's phone, avoiding such a fraud| M | +|Roles, Actor(s) and scope|Bank Application: role of Call Forwarding Signal API consumer
                                                      API Provider: role of Call Forwarding Signal API provider
                                                      End User: role of owner of the phone number to be verified
                                                      Scope: Anti fraud| M | +|NF Requirements|| O | +|Pre-conditions|• The Bank Application is aware of the End User's phone number
                                                      • The End User gave the consent to check for the Call Forwarding Service activation on his phone number.| M | +|Begins when|The Bank Application invokes the Call Forwarding Signal API to get the information on the status of the Unconditional Call Forwarding Service for his End User's phone number.| M | +|Step 1|The API Provider identifies the Bank Application as a valid Call Forwarding Signal API Consumer| M | +|Step 2|The API Provider verifies the User Consent| M| +|Step 3|The Bank Application invokes the Call Forwarding Signal API Producer providing the End User's phone number asking for the status of the Unconditional Call Forwarding Service | M | +|Step 4|The Call Forwarding Signal API Producer checks if the End User's phone number has an active Unconditional Call Forwarding Service| M | +|Ends when|The Call Forwarding Signal API Producer notifies the Bank Application about the status of the Unconditional Call Forwarding Service| M | +|Post-conditions|The Bank Application is aware of the status for the Unconditional Call Forwarding Service for the End User's phone number | M | +|Exceptions|Step 4 can generate an exception to be notified to the Bank Application| M | diff --git a/original/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist.md b/original/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..8eecf49bc9b362f118de21c5eadee9b72c0f5623 --- /dev/null +++ b/original/CallForwardingSignal/documentation/API_documentation/call-forwarding-signal-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ + +# API Readiness Checklist + +Checklist for API call-forwarding-signal v0.4.0 in r3.3 + + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/call-forwarding-signal.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.4.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/CFS_UserStory_UseCase-1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [call-forwarding-signal-every-forwarding](/code/Test_definitions/call-forwarding-signal-every-forwarding.feature), [call-forwarding-signal-unconditional](/code/Test_definitions/call-forwarding-signal-unconditional.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [call-forwarding-signal-every-forwarding](/code/Test_definitions/call-forwarding-signal-every-forwarding.feature), [call-forwarding-signal-unconditional](/code/Test_definitions/call-forwarding-signal-unconditional.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/uoDVB) | + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/original/CallForwardingSignal/documentation/MeetingMinutes/README.md b/original/CallForwardingSignal/documentation/MeetingMinutes/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9a8057c76ce98e88296ed7f22512dbab7606356f --- /dev/null +++ b/original/CallForwardingSignal/documentation/MeetingMinutes/README.md @@ -0,0 +1,5 @@ +## Meeting Minutes of Call Forwarding Signal Sub Project + +Starting with the beginning of 2024 the meeting minutes of Call Forwarding Signal calls are within the CAMARA Wiki at: + +https://wiki.camaraproject.org/display/CAM/SP-CFS+Minutes diff --git a/original/CallForwardingSignal/documentation/SupportingDocuments/README.MD b/original/CallForwardingSignal/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/CallForwardingSignal/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/CapabilitiesAndRuntimeRestrictions/README.md b/original/CapabilitiesAndRuntimeRestrictions/README.md new file mode 100644 index 0000000000000000000000000000000000000000..278aec5b49319ea2e198f54cfd0f63d1a8645f6d --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/README.md @@ -0,0 +1,43 @@ + + + + + + + + + +# CapabilitiesAndRuntimeRestrictions + +Sandbox API Repository to describe, develop, document, and test the CapabilitiesAndRuntimeRestrictions Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/6YAjAw) + +## Scope + +* Service APIs for “CapabilitiesAndRuntimeRestrictions” (see APIBacklog.md) +* The CAMARA Runtime Restrictions API allows API consumers to understand and adapt to environment-specific differences in how CAMARA APIs are implemented. It provides details on what is supported, what is temporarily unavailable, and any other limitations that might affect how you call and consume those APIs. This API provides that information about other CAMARA APIs. +* The API provides the API consumer with the ability to: + * Discover Capabilities and Constraints + * Stay updated on changes + * Adapt your requests Automatically +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Tuesdays 1400-1500 UTC, every two weeks. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96678356438?password=706020d3-07bc-4d90-a0d5-1d6b94452a53) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/6YAjAw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . + diff --git a/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README.MD b/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi.yaml b/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi.yaml new file mode 100644 index 0000000000000000000000000000000000000000..5f4a2867e0019ab05a2f41426496d49189a0d369 --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/code/API_definitions/camara-service-capability-openapi.yaml @@ -0,0 +1,1373 @@ +--- +openapi: 3.0.3 +info: + title: CAMARA Service Capability API + description: | + The CAMARA Service Capability API provides programmable interface for developers and other users (capabilities consumers) to discover and be notified + about active/inactive capabilities (functions) for APIs. + + It delivers a tailored service capability based on consumer context, supporting complex request bodies, endpoint removal, and dynamic restrictions. + + # Introduction + This API enables feature discovery and near-real-time feature status notifications for APIs provided by the gateway / provider. + + Overlay-based restrictions use JSON Schema Validation (draft-bhutton-json-schema-validation-01) keywords and ensure restriction-only constraints. + The specification supports dynamic tailoring via `POST /camara/service/capability/v0`, which returns a restriction mapping with bit positions, capability identifiers, + and a mapping version. Initial restriction states are included in the successful response. Restriction state changes are notified via CloudEvents using bitmap-only + payloads for restrictions and leveraging the restriction mapping for synchronization. Versioning ensures consumers adapt to mapping changes. + + Overlays conform to the OpenAPI Overlay specification (https://spec.openapis.org/overlay/latest.html) and are evaluated at run-time rather than build-time on API consumer side using + context-aware logic. Only schema-restrictive updates are allowed (e.g., narrowing enums, removing operations). These extensions enable fine-grained control over API capabilities + by applying restriction-only constraints to schemas, body fields, and headers/parameters, respectively. + + An **API** (Application Programming Interface) often includes **features** that can be *active* or *inactive* during + interactions with API consumers. For example, feature negotiation during session establishment or events such as high congestion that + change a feature's status. + + **Capabilities** represent a collection of features and their **status** (*active* or *inactive*) at runtime. + These capabilities provide a way to describe what an API can do. + + **Footprints** define the coverage area where specific capabilities are available. A device must be located within the footprint to access + these capabilities. If no footprint is specified, the capabilities *may* be available to *any* device connected to the network. Footprints + have a *usage type* that determines their visibility and use. For example, some footprints may only be visible to Access Networks where + devices are attached, while others may be visible to Internet servers or services in a Non-Access network. Some footprints + may even be used in both types of networks. + + The API provider MAY have full knowledge of whereabout of the device, thus directly notifying the capabilities consumers + with near-real-time capability changes resulting of device location change without using footprints. This would reduce the additional footprint processing requirement at the consumer side + when the device receives the capability notification and capability info. + + When footprints are used, they are presented as part of a collection. A device is considered to be covered by a footprint collection if it + falls within at least one footprint in the collection. Footprint *precedence* specifies the search execution order of footprints in the + collection. The lower the numerical value of precedence, the higher the footprint precedence. Footprints with equal precedence MAY be + executed in parallel if supported by the system. (see *Usage* for more detail). + + To convey the impact of capability status to API consumers in a meaningful way, capabilities are directly tied to a set of **Runtime Restrictions**. + These restrictions affect optional or alternative structures, parameters, and other aspects of API usage. + + # Usage + The Camara Service Capability API enables clients to discover and manage CAMARA API capabilities + through a simple, RESTful interface and receive automatic CloudEvents when state changes. + ```mermaid + Client Webhook/Sink Capability API CloudEvents Broker + | | | | + |---------------------------------------->| | + | POST /camara/service/capability/v0 | | + |<----------------------------------------| | + | 201 + CapabilityInfo | | + | | | | + | | |----------------------> | + | | | Create Subscription | + | | | for capability | + | | | changes | + | | |----------------------->| + | | | Capability Changed | + | |<-------------------------------------------| + | | POST CloudEvent to Webhook | + | | | | + | |------------------------------------------->| + | | 204 | + | | | | + The Capability API responds with the supported capabilities and then internally + registers for capability change events if 'subscriptionRequest' is provided in the request. + As capabilities change event notifications are forwarded through a CloudEvents Broker to + the client-provided Webhook (Sink). + ``` + **How it works** + 1. **Query capabilities** + Client sends one or more `CamaraCapabilityQuery` objects to `/camara/service/capability/v0`. + 2. **Inspect response** + API returns a `CapabilityInfo` object with per-capability details, overlays, and restriction sets. + 3. **Receive updates automatically** + Whenever capability bitmaps or info change, the API emits a CloudEvent (via implicit subscription) + to your configured webhook sink endpoint. + **Supported CloudEvent types:** + - `org.camaraproject.capability.v0.capability-bitmap-changed` + - `org.camaraproject.capability.v0.capability-info-changed` + For full schema definitions and examples, see the components section below. + + ### Summary: + 1. `POST /camara/service/capability/v0`: Returns tailored CapabilityBitmap that assigns bit positions of each restriction, a mappingVersion for versioning for new restrictions. + 2. CloudEvents Notifications: Signals restriction state changes (active/inactive) via bitmap change event and new restrictions via info change event, ensuring efficient synchronization. + 3. Versioning: Uses mappingVersion to handle changes in the restriction mapping, preventing synchronization errors. + + # Relevant terms and definitions + * **Authentication**: + Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the Capability API. + * **API (Application Programming Interface)**: + A set of protocols and tools for building software and applications. + * **Features**: + Specific functions or capabilities of an API that can be *active* or *inactive*. + * **Capabilities**: + A collection of features and their status (*active* or *inactive*) at a specific point in time. + * **Footprints**: + Define the coverage area where specific capabilities are available. + * **Runtime Restrictions**: + Restrictions that affect optional or alternative structures, parameters, and other aspects of API usage using a collection of overlays. + There are two kinds of overlays. The openAPI Overlays specification is at https://spec.openapis.org/overlay/latest.html. + One kind is the static version of overlays which can be applied to the API spec at the build time of the + Client. The actions of the overlays are known to the Client before any runtime. Second kind is the one we're specifying in this CAMARA + Service Capability API specification where the overlays take effect at the runtime of the Client if the Client supports this specification. + The actions of any overlays are not known to the Client until they're communicated from the API provider at the runtime of the Client. + + # API functionality + Please see examples within this yaml on what options the gateway may return in the response. + + # Further info and support + + ## Frequently Asked Questions (FAQs) + 1. What is the purpose of the API described in the text? + The API enables feature discovery and near-real-time feature status notifications + for APIs provided by the gateway. + 2. What are capabilities and how do they relate to API features? + Capabilities represent a collection of features and their + status (*active* or *inactive*) at a specific point in time. These capabilities provide a way to describe what an API can do. + 3. What are footprints and how do they affect the availability of capabilities? + Footprints define the coverage area where specific + capabilities are available. A device must be located within the footprint to access these capabilities. If no footprint is specified, + the capabilities may be available to any device connected to the network. + 4. What is the role of footprint precedence in the search execution order? + Footprint precedence specifies the search execution order of + Footprints in the collection. The lower the numerical value of precedence, the higher the Footprint precedence. Footprints with equal + precedence may be executed in parallel if supported by the system. + 5. How do runtime restrictions affect API usage? + To convey the impact of capability status to API consumers in a meaningful way, + capabilities are directly tied to a set of runtime restrictions. These restrictions affect optional or alternative structures, + parameters, and other aspects of API usage using a collection of overlays. + 6. What if a Client does not support this API? + They can send requests without using this API. The downside + is that they may send requests that are invalid and could have been avoided with information from this API. They + could be more proactive by disabling / hiding options that are not enabled in the Client which improves user + experience. + 7. What if a Client does not support Footprints or a specific Footprint type? + They should ignore enforcing the + state of the specific capability. This may result in sending invalid requests. + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +servers: + - url: '{apiRoot}/camara-service-capability-openapi/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: CAMARA Service Capability Query + description: Returns the Service Capability for specified CAMARA service APIs + on the API gateway / producer side. + - name: CAMARA Service Capability notifications callback + description: Callback endpoint for receiving notifications on capability changes. +paths: + /camara/service/capability/v0: + post: + tags: [CAMARA Service Capability Query] + summary: Retrieve tailored service capabilities based on consumer context + description: | + Returns service capability information tailored to the consumer's context, including active/inactive restrictions and mapping metadata. + Successful response is with sets of restrictions based on consumer context, along with a restriction mapping assigning bit positions, + capability identifiers, and a mapping version. It includes response with initial bitmaps which should be enforced on the API consumer side. + operationId: postServiceCapability + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/If-None-Match' + - $ref: '#/components/parameters/If-Modified-Since' + security: + - openId: [camara-capability:read] + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CamaraCapabilityQueryRequest' + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE: + $ref: '#/components/examples/CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE' + callbacks: + notifications: + '{$request.body#/subscriptionRequest/sink}': + post: + tags: [CAMARA Service Capability notifications callback] + summary: CAMARA Service Capability notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any CAMARA Service Capability change related event occurs. + Currently only EVENT_CAPABILITY_CHANGED and EVENT_CAPABILITY_REMOVED events are defined. + operationId: postCapabilityNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents-batch+json: + schema: + type: array + items: + $ref: '#/components/schemas/CloudEvent' + examples: + EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE: + $ref: '#/components/examples/EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE' + EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE: + $ref: '#/components/examples/EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE' + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + security: + - notificationsBearerAuth: [] + responses: + '201': + description: Tailored Capability info with current restriction mapping + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + ETag: + $ref: '#/components/headers/ETag' + Cache-Control: + $ref: '#/components/headers/Cache-Control' + Last-Modified: + $ref: '#/components/headers/Last-Modified' + content: + application/json: + schema: + $ref: '#/components/schemas/CapabilityInfo' + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE: + $ref: '#/components/examples/CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE' + '304': + $ref: '#/components/responses/CapabilityNotModified304' + '400': + $ref: '#/components/responses/CapabilityApiBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/CapabilityApiNotFound404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + $ref: ../common/CAMARA_common.yaml#/components/securitySchemes/openId + notificationsBearerAuth: + $ref: ../common/CAMARA_common.yaml#/components/securitySchemes/notificationsBearerAuth + parameters: + x-correlator: + $ref: ../common/CAMARA_common.yaml#/components/parameters/x-correlator + If-None-Match: + $ref: ../common/CAMARA_common.yaml#/components/parameters/If-None-Match + If-Modified-Since: + $ref: ../common/CAMARA_common.yaml#/components/parameters/If-Modified-Since + headers: + x-correlator: + $ref: ../common/CAMARA_common.yaml#/components/headers/x-correlator + Cache-Control: + $ref: ../common/CAMARA_common.yaml#/components/headers/Cache-Control + ETag: + $ref: ../common/CAMARA_common.yaml#/components/headers/ETag + Last-Modified: + $ref: ../common/CAMARA_common.yaml#/components/headers/Last-Modified + schemas: + # General items used throughout the specification + Contexts: + description: | + An extensible container for reusable objects referenced by Overlays. It may reflect state of the API Service, client state, etc. + type: object + properties: + url: + type: string + format: uri + description: The resolved request URL. + method: + type: string + description: HTTP method in upper-case. + request: + $ref: '#/components/schemas/HttpMessage' + additionalProperties: true + required: [url, method, request] + HttpMessage: + type: object + description: Common structure for $request and, if supported, $response. + properties: + header: + type: object + # Valid header *names* (field-name = token) + description: | + A map of HTTP header fields. + **Header names (object keys)** SHOULD conform to the RFC-7230 `token` syntax: + `^[!#$%&'*+\-\.^_`|~0-9A-Za-z]+$` + Note: OpenAPI 3.0.3 cannot enforce key-name patterns natively. + additionalProperties: + type: string + pattern: ^[\t\x20-\x7E\x80-\xFF]*$ + description: Value of the header field (matches `field-value` ABNF) + query: + type: object + description: Query-string parameters; keys are already decoded. + additionalProperties: true + path: + type: object + description: Captured path parameters. + additionalProperties: true + body: + description: Request or response payload. Its shape depends on Content-Type. + additionalProperties: false + VersionedName: + description: | + An abstract base object containing names with versioning + type: object + properties: + name: + description: The item's name. Ideally, it is a unique value for its type. + This value MUST NOT contain the semicolon - ';' + type: string + example: cap1 + minLength: 3 + maxLength: 256 + pattern: ^[^;]*$ + version: + description: | + The semantic version of the object instance following [SemVer 2.0.0](https://semver.org/). + Examples: + - `1.0.0` + - `2.3.1-beta` + - `1.4.5+build.2025` + type: string + example: 1.0.0 + minLength: 1 + pattern: ^(0|[1-9]\d*)\.(0|[1-9]\d*)\.(0|[1-9]\d*)(?:-((?:0|[1-9]\d*|\d*[A-Za-z-][0-9A-Za-z-]*)(?:\.(?:0|[1-9]\d*|\d*[A-Za-z-][0-9A-Za-z-]*))*))?(?:\+([0-9A-Za-z-]+(?:\.[0-9A-Za-z-]+)*))?$ + specifyingBody: + description: Entity's specification organization (reversed fqdn format) + type: string + minLength: 1 + required: [name, version] + Footprint: + description: | + The coverage area to which capabilities apply. They help define the context in which the features are relevant. + There are many ways to describe a footprint -- for example, by address range (e.g., IPv4 CIDR or IPv6 CIDR (Classless Inter-Domain Routing), + network ID (e.g., Autonomous System Number (ASN)), nation boundaries (e.g., country code) or GPS coordinates. + When a **Footprint** value is not present, the capabilities apply to *any* connected device. + allOf: + - $ref: '#/components/schemas/VersionedName' + - type: object + properties: + footprintType: + description: | + Types include: + * [Content Delivery Network Interconnection](https://www.iana.org/assignments/cdni-parameters/cdni-parameters.xhtml#metadata-footprint-types) types + * [Geo position](https://www.iana.org/assignments/method-tokens/method-tokens.xhtml) types + * [Civic Address](https://datamodel.tmforum.org/en/latest/Common/Address/) types + * [Geographic Address type](https://github.com/tmforum-apis/TMF673_GeographicAddress) types + * [Geographic Location type](https://github.com/tmforum-apis/TMF675_GeographicLocation) types + * [Geographic Site type](https://github.com/tmforum-apis/TMF674_GeographicSite) types + * [ITU E.212 Mobile Country Code and Mobile Network Code](https://en.wikipedia.org/wiki/Mobile_country_code) values + * [GeoJSON](https://github.com/geojson/schema) + * [TopoJSON](https://github.com/topojson/topojson) + * [IP Geolocation Feeds (geofeed)](https://datatracker.ietf.org/doc/rfc8805/) + type: string + enum: + - ipv4cidr + - ipv6cidr + - asn + - countrycode + - altopid + - subdivisioncode + - footprintunion + - civicaddress + - geoposition + - itue212countrynetworkcode + - postaladdress + - geographicaddress + - geographiclocation + - geographicsite + - geojson + - topojson + - geofeedRFC8805 + footprintValue: + description: A list of footprint values. + type: array + items: + oneOf: + - type: string + - type: object + footprintUsage: + description: Indicates that the footprint value represents an Access + Network, a non Access Network, i.e., networks facing the Internet, + or both. + type: string + enum: [access, non_access, both] + precedence: + description: | + Specifies the search execution order of Footprints when they are part of a collection. The lower the numerical value of precedence, + the higher the rule precedence. Rules with equal precedence MAY be executed in parallel if supported. + type: integer + minimum: 0 + required: + - name + - version + - footprintType + - footprintValue + - footprintUsage + - precedence + Metadata: + description: > + Tighten validation, avoid client/server drift, and make structures robust. + type: object + properties: + description: + type: string + description: Human-readable description of the entity + createdAt: + type: string + format: date-time + description: | + RFC 3339 timestamp when this mapping was first published. + Providers must not set times in the future. + example: '2025-05-09T14:25:38Z' + lastModifiedAt: + type: string + format: date-time + description: | + RFC 3339 timestamp of the last non-breaking update. + Providers must not set times in the future. + example: '2025-05-10T12:03:00Z' + deprecatedAt: + type: string + format: date-time + description: RFC 3339 timestamp after which this entity is no longer be + applicable. + mappingHash: + type: string + pattern: ^[A-Fa-f0-9]{64}$ # SHA-256 in hex + description: SHA-256 digest of the canonical JSON representation of this + mapping. + example: 5d41402abc4b2a76b9719d911017c592cf0c58f2b3b65af6f88ab3a2b4d6996f + traceID: + type: string + description: Trace Identifier used across multiple systems. + + # Overlay imports + Overlay: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Overlay + Action: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Action-Object + Extends: + $ref: ../modules/overlay-openapi.yaml#/components/schemas/Extends + + # Camara extensions to Open API Overlay components + CamaraOverlay: + description: | + Common attributes of a CAMARA Overlay. + It extends OpenAPI Overlay Specification v1.0.0 for restriction-only schema patches. + allOf: + - $ref: '#/components/schemas/Overlay' + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + - type: object + properties: + actions: + description: A ordered list of actions + type: array + minItems: 1 + maxItems: 20 # DoS - guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CamaraAction' + operator: + description: | + Logical operator combining the results of all actions: + - **and**: all actions must succeed; processing stops on first failure + - **or**: failed actions are skipped + type: string + enum: [and, or] + default: and + required: [name, version, actions] + CamaraAction: + type: object + description: | + Extends a standard Overlay Action-Object by + a. refining update to ONLY accept SchemaRestriction + b. letting the API provider pre-compute exactly which nodes will be + affected, using either JSON Pointers or OpenAPI runtime expressions. + This makes it possible to: + 1. **target** an OpenAPI document fragment (via JSONPath). + 2. **Resolve** that target against an instance of the Open API schema + into one or more concrete locations—each expressed as either a JSON Pointer + or an OpenAPI runtime expression. + 3. **Apply** the `update` or `remove` action deterministically to those + resolved locations. + By including `targetLocations`, clients can skip the extra step of evaluating + `target` themselves against instances of the schema, ensuring precise, + unambiguous application and enabling robust validation through attached `SchemaRestrictions`. + When targetLocations is present, any target value MUST be ignored. + allOf: + - $ref: '#/components/schemas/Action' + properties: + id: + type: string + description: Identifier for this action. Used for tracability. Each id MUST + be unique within the overlay. + targetLocations: + description: | + A non-empty list of explicit document locations—specified as a + InstanceLocation. These values override the generic `target` + selector. + + All entries MUST use the same syntax (Runtime Expression or JSON Pointer). + type: array + minItems: 1 + maxItems: 30 + items: + $ref: '#/components/schemas/InstanceLocation' + # refinement of update - it can only take on + update: + description: update of schema restrictions + type: object + additionalProperties: + $ref: '#/components/schemas/SchemaRestrictions' + instanceUpdate: + description: An update of an instance document's value. + type: object + instanceRemove: + description: A boolean indicating the result's value should be removed from + the instance's document. + type: boolean + forceAction: + type: boolean + description: | + When **true**, and **restrictions** are satisfied, the specified + **instanceUpdate** or **instanceRemove** MUST be enforced (no silent failures). + If **forceAction** is present, either **instanceUpdate** or **instanceRemove** + MUST also be present. + default: true + example: true + # validation logic + anyOf: # target or targetLocations MUST be present + - required: [target] + - required: [targetLocations] + not: # instanceUpdate and instanceRemove MUST NOT be present at the same time + required: [instanceUpdate, instanceRemove] + # When forceAction is present, instanceUpdate or instanceRemove MUST be present + oneOf: + # Case A: forceAction is *not* present (nothing else enforced) + - not: + required: [forceAction] + # Case B: forceAction *is* present, and exactly one payload must accompany it + - allOf: + - required: [forceAction] + - oneOf: + - required: [instanceUpdate] + - required: [instanceRemove] + InstanceLocation: + description: | + A location in the JSON document that is an instance of an OpenAPI Schema. + It provides an optional endpoint to restrict it as well as the location. + All strings follow a Open API Runtime Expression or JSON Pointer (RFC 6901) format. + type: object + properties: + endpoint: + description: Optional endpoint path of a URI that MUST be present in the + request/response. + allOf: + - $ref: '#/components/schemas/InstanceLocationSyntax' + location: + description: The location of the target result. + allOf: + - $ref: '#/components/schemas/InstanceLocationSyntax' + additionalProperties: false + required: [location] + InstanceLocationSyntax: + description: A string whose format is Open API Runtime Expression or JSON Path. + type: string + minLength: 1 + oneOf: + - x-camara-targetSyntax: runtimeexpression # runtime expression + pattern: ^\$(?:url|method|statusCode|request\.(?:header\.[!#$%&'*+\-\.\^_`|~0-9A-Za-z]+|query\.[^\s\/]+|path\.[^\s\/]+|body(?:#\/(?:[^\/~]|~0|~1)+(?:\/(?:[^\/~]|~0|~1)+)*)?)|response\.(?:header\.[!#$%&'*+\-\.\^_`|~0-9A-Za-z]+|body(?:#\/(?:[^\/~]|~0|~1)+(?:\/(?:[^\/~]|~0|~1)+)*)?)) + minLength: 1 + - x-camara-targetSyntax: jsonPointer # JSON Pointer + pattern: ^(/([^/~]|~[01])*)*$ + minLength: 1 + SchemaRestrictions: + description: | + A set of schema constraints evaluated against a single target. + - **restrictions** - An array (min = 1) of `SchemaRestriction` objects. + Each restriction returns a Boolean result when applied to the target. + - **operator** - Optional logical operator that combines the restriction + results. Supported values are: **and** (default), **or**, **not**. + When a single restrictions is supplied, **not** negates that result. + If `operator` is omitted, **and** is assumed. + If only one restriction is present, `operator: not` will negate it. Values of `operator: and` and + `operator: or` are ignored. + If `operator` is present, `restrictions` **MUST** also be present. + type: object + properties: + restrictions: + description: An array of `SchemaRestriction` objects. + type: array + minItems: 1 + uniqueItems: true + items: + $ref: '#/components/schemas/SchemaRestriction' + operator: + description: | + Logical operator that combines the results of all restrictions. + - **and** - All restrictions MUST be true. + - **or** - At least one restriction MUST be true. + - **not** - No restriction MAY be true. For a single restriction this simply negates the result. + type: string + enum: [and, or, not] + default: and + required: [restrictions] + SchemaRestriction: + description: | + Single schema update that refines and restricts the target. + This update **MUST** be compatible with the referenced target. + type: object + anyOf: + - $ref: '#/components/schemas/SchemaRestrictionMeta' + - $ref: '#/components/schemas/SchemaRestrictionAnyInstance' + - $ref: '#/components/schemas/SchemaRestrictionNumeric' + - $ref: '#/components/schemas/SchemaRestrictionString' + - $ref: '#/components/schemas/SchemaRestrictionArray' + - $ref: '#/components/schemas/SchemaRestrictionObject' + - $ref: '#/components/schemas/SchemaRestrictionParameter' + - $ref: '#/components/schemas/SchemaRestrictionOperation' + - $ref: '#/components/schemas/SchemaRestrictionPresence' + SchemaRestrictionMeta: + type: object + description: > + Restriction applicable to any target at runtime. + Based upon the JSON Schema [A Vocabulary for Basic Meta-Data Annotations](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-a-vocabulary-for-basic-meta). + additionalProperties: false + properties: + deprecated: {type: boolean, description: Mark as deprecated.} + readOnly: {type: boolean, description: Mark as read-only.} + writeOnly: {type: boolean, description: Mark as write-only.} + default: {type: string, description: Default value to apply.} + SchemaRestrictionAnyInstance: + type: object + description: > + Restriction applicable to any target at runtime. + Based upon the JSON Schema [Validation keywords for Any instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-any). + additionalProperties: false + properties: + type: + type: string + enum: [boolean, object, array, number, string, integer] + nullable: true + description: > + Restrict the type of the value. Only applicable when the type was + not initially specified or matches the target's current type. + enum: + type: array + items: {type: string} + description: Restrict allowed values (must be a subset of the original enum). + const: + type: string + description: Force the field to have a constant value. + SchemaRestrictionNumeric: + type: object + description: > + Restriction applicable to numeric ranges (for example min/max values). + Based upon the JSON Schema [Validation keywords for Numeric Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-num). + additionalProperties: false + properties: + multipleOf: {type: number, minimum: 1, description: Value MUST be a multiple + of this number.} + maximum: {type: number, description: Value MUST be less than or equal to this + number.} + minimum: {type: number, description: Value MUST be greater than or equal to + this number.} + exclusiveMaximum: {type: number, description: Value MUST be strictly less + than this number.} + exclusiveMinimum: {type: number, description: Value MUST be strictly greater + than this number.} + SchemaRestrictionString: + type: object + description: > + Restriction applicable to string fields (length or pattern). + Based upon the JSON Schema [Validation keywords for Strings](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-str). + additionalProperties: false + properties: + maxLength: {type: integer, minimum: 0, description: Maximum string length.} + minLength: {type: integer, minimum: 0, description: Minimum string length.} + pattern: {type: string, description: Regular-expression pattern the string + MUST match.} + SchemaRestrictionArray: + type: object + description: > + Restriction applicable to arrays (size or uniqueness). + Based upon the JSON Schema [Validation keywords for Array Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-arr). + additionalProperties: false + properties: + maxItems: {type: integer, minimum: 0, description: Maximum number of items.} + minItems: {type: integer, minimum: 0, description: Minimum number of items.} + uniqueItems: {type: boolean, description: 'If **true**, all items MUST be + unique.'} + maxContains: {type: integer, minimum: 0, description: Maximum count for items + that match the `contains` schema.} + minContains: {type: integer, minimum: 0, description: Minimum count for items + that match the `contains` schema.} + SchemaRestrictionObject: + type: object + description: > + Restriction applicable to object structures. + Based upon the JSON Schema [Validation keywords for Object Instances](https://www.ietf.org/archive/id/draft-bhutton-json-schema-validation-01.html#name-validation-keywords-for-obj). + additionalProperties: false + properties: + maxProperties: {type: integer, minimum: 0, description: Maximum number of + object properties.} + minProperties: {type: integer, minimum: 0, description: Minimum number of + object properties.} + required: + type: array + items: {type: string} + description: List of required properties (MUST already exist in the schema). + dependentRequired: + type: array + items: {type: string} + description: '[`dependentRequired`](https://json-schema.org/draft/2020-12/json-schema-validation#name-validation-keywords-for-obj)' + excludedProperties: + type: array + items: {type: string} + description: Properties that MUST be absent. + SchemaRestrictionParameter: + type: object + description: > + Restriction that applies only to HTTP request parameters (e.g. query + parameters). + Based upon the OpenAPI *Parameter Object* and provides: + - Mandating the use of an optional parameter - Allowing empty values + additionalProperties: false + properties: + allowEmptyValue: + type: boolean + description: > + Permits empty values. MAY be **true** only if the original schema + did not explicitly specify `allowEmptyValue: false`. + mandatory: + type: boolean + description: > + Mandates the use of an otherwise-optional parameter. Allowed only + when: 1. The original schema does **not** declare `deprecated: true`, + and 2. The original schema does **not** set `mandatory` to the opposite + value. + SchemaRestrictionOperation: + type: object + description: > + Restriction that applies to an absolute or relative path (operation). + Based upon the OpenAPI *Operation Object* and provides: + - `notImplemented` - `notAvailable` + additionalProperties: false + properties: + notImplemented: + type: boolean + description: Marks the operation as unimplemented. Invocation MUST return + **501 Not Implemented**. + notAvailable: + type: boolean + description: Marks the operation as temporarily unavailable. Invocation + MUST return **503 Service Unavailable**. + SchemaRestrictionPresence: + type: object + description: > + Restriction that applies to runtime presence of the target. + properties: + presence: + type: boolean + description: > + When **true**, at least one instance matching the target JSON Pointer + or JSON Path **MUST** be present. When **false**, no such instance **MAY** + be present. + SchemaRestrictionsSet: + description: Base restriction type + type: object + allOf: + - $ref: '#/components/schemas/VersionedName' + properties: + restrictions: + description: restrictions + type: array + uniqueItems: true + minItems: 1 + maxItems: 10 + items: + $ref: '#/components/schemas/CamaraOverlay' + footprints: + description: footprints + type: array + uniqueItems: true + minItems: 1 + maxItems: 10 + items: + $ref: '#/components/schemas/Footprint' + resourceServers: + description: resourceServers + type: array + uniqueItems: true # no duplicates + maxItems: 10 + items: + type: string + format: uri # ensures each locator is a valid URI + required: [restrictions] + + # Camara capability structures + CapabilityBitmap: + description: Common attributes of CAMARA capability bitmap + type: object + allOf: + - $ref: '#/components/schemas/CamaraCapabilityQuery' + properties: + mappingVersion: + type: string + description: Version of the capability to restriction mapping, used to detect + changes. + example: 1.0.0 + camaraCapabilitiesBitmap: + description: | + Bitmap value of the capabilities to show current state (active or inactive) of the RestrictionSet. + Decimal representation of a binary bitmask indicating active capabilities. + This integer should be interpreted as a binary string (bitfield), where: + - The **least significant bit (rightmost bit)** corresponds to key **"0"** in the `bitmapCapabilities` object. + - The next bit to the left corresponds to key **"1"**, and so on. + - Bit at position `n` (counting from right, 0-based) maps to key `"n"`. + For example: + - If `CapabilityBitmap` = `13`, the binary form is `1101`. + - Interpreted as: + - Bit 0 (LSB, rightmost) → "0" → active + - Bit 1 → "1" → inactive + - Bit 2 → "2" → active + - Bit 3 (MSB) → "3" → active + - This means `bitmapCapabilities["0"]`, `["2"]`, and `["3"]` apply. + Implementors of API provider should preserve this bit order when interpreting or generating the bitmask, so that capability indices remain consistent over time. + type: integer + minimum: 0 + format: int64 + maximum: 18446744073709551615 + example: 6 + required: [mappingVersion, camaraCapabilitiesBitmap] + CapabilityInfo: + description: A list of CapabilityDetail. + type: object + properties: + details: + description: a list of CapabilityDetail. + type: array + minItems: 1 + maxItems: 1000 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CapabilityDetail' + CapabilityDetail: + description: | + A self-contained snapshot of what each capability means (CapabilityBitmap) and its current active/inactive state. + When these are CapabilitySetFootprint the state is always active. + When it is CapabilitySetBitmap, then CapabilityBitmap is included that conveys the active/inactive state of each + bit position. + type: object + anyOf: + - $ref: '#/components/schemas/CapabilitySetFootprint' + - allOf: + - $ref: '#/components/schemas/CapabilitySetBitmap' + - $ref: '#/components/schemas/CapabilityBitmap' + minProperties: 1 + CapabilitySetFootprint: + description: | + Associates a capability with one or more RestrictionSets that + defined by footprint constraints. + type: object + additionalProperties: false # reject typos / undocumented fields + allOf: + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + properties: + footprints: + description: An array of restrictions that apply when the endpoint is present + in one of the entry's footprints. + type: array + minItems: 1 + maxItems: 64 + uniqueItems: true + items: + allOf: + - $ref: '#/components/schemas/SchemaRestrictionsSet' + - required: [footprints] + required: [footprints] + CapabilitySetBitmap: + description: | + Associates a capability with one or more RestrictionSets + define through a bitmap position. + type: object + allOf: + - $ref: '#/components/schemas/VersionedName' + - $ref: '#/components/schemas/Metadata' + properties: + bitmapCapabilities: + type: object + description: > + Map of bitPosition → SchemaRestrictionsSet. Keys are stringified bitPosition + indices (duplicates impossible). **Header names (object keys)** SHOULD + consist of one or more digits, matching `^[0-9]+$`. (Note: OpenAPI 3.0.3 + cannot enforce key-name patterns natively.) + additionalProperties: + $ref: '#/components/schemas/SchemaRestrictionsSet' + required: [bitmapCapabilities] + + # API related information + CamaraCapabilityQueryRequest: + description: A list of queries in the request. + type: object + additionalProperties: true + properties: + queries: + description: A list of CamaraCapabilityQuery + type: array + minItems: 1 + maxItems: 100 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/CamaraCapabilityQuery' + subscriptionRequest: + $ref: '#/components/schemas/CamaraExtendedSubscriptionRequest' + required: [queries] + CamaraCapabilityQuery: + description: Common attributes of CAMARA capability query + type: object + properties: + resourceScopes: + $ref: '#/components/schemas/ResourceScopes' + overlayExtends: + description: list of unique overlay extends in the query + type: array + minItems: 1 + maxItems: 20 # DoS guard rail + uniqueItems: true + items: + $ref: '#/components/schemas/Extends' + required: [overlayExtends] + ResourceScopes: + $ref: ../common/CAMARA_common.yaml#/components/schemas/ResourceScopes + ErrorInfo: + $ref: ../common/CAMARA_common.yaml#/components/schemas/ErrorInfo + + # Event structures + CamaraExtendedSubscriptionRequest: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraExtendedSubscriptionRequest + org.camaraproject.capability.v0.detail: + description: The detail of the requested capability event subscription. + type: object + allOf: + - $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/SubscriptionDetail + - type: object + properties: + resourceScopes: + $ref: '#/components/schemas/ResourceScopes' + additionalProperties: false + CloudEvent: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraExtendedCloudEventsAttribute + CloudEventData: + $ref: ../common/CAMARA-subscriptions-openapi.yaml#/components/schemas/CamaraCloudEventData + org.camaraproject.capability.v0.capability-bitmap-changed: + description: Event structure for capability bitmap changed + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/org.camaraproject.capability.v0.capability-bitmap-changed.data' + required: [data] + additionalProperties: false + example: + $ref: '#/components/examples/EVENT_CAPABILITY_BITMAP_CHANGED_EXAMPLE/value' + org.camaraproject.capability.v0.capability-bitmap-changed.data: + description: Event for capability bitmap changed + allOf: + - $ref: '#/components/schemas/CloudEventData' + - type: object + properties: + capabilityBitmap: + $ref: '#/components/schemas/CapabilityBitmap' + required: [capabilityBitmap] + additionalProperties: false + org.camaraproject.capability.v0.capability-info-changed: + description: Event structure for capability info changed + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/org.camaraproject.capability.v0.capability-info-changed.data' + required: [data] + additionalProperties: false + example: + $ref: '#/components/examples/EVENT_CAPABILITY_INFO_CHANGED_EXAMPLE/value' + org.camaraproject.capability.v0.capability-info-changed.data: + description: Event for capability info changed + allOf: + - $ref: '#/components/schemas/CloudEventData' + - type: object + properties: + capabilityInfo: + $ref: '#/components/schemas/CapabilityInfo' + required: [capabilityInfo] + additionalProperties: false + responses: + CapabilityNotModified304: + description: Not Modified (cached response) + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Generic400: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic400 + CapabilityApiBadRequest400: + description: Bad Request when query capability + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + title: CapabilityApiBadRequest400 + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: [400] + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query + param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given + field has a pre-defined range or a invalid filter criteria combination + is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + Generic401: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic401 + Generic403: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic403 + Generic404: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic404 + CapabilityApiNotFound404: + description: Capability API not found + content: + application/json: + schema: + title: CapabilityApiNotFound404 + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: [404] + code: + enum: [NOT_FOUND] + example: + status: 404 + code: NOT_FOUND + message: No Capability API found + Generic409: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic409 + Generic410: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic410 + Generic429: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic429 + Generic500: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic500 + Generic503: + $ref: ../common/CAMARA_common.yaml#/components/responses/Generic503 + examples: + CAMARA_CAPABILITY_QUERY_REQUEST_EXAMPLE: + summary: Example of capability query + description: query capability request + value: + queries: + - resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + subscriptionRequest: + sink: https://application-server.com/notifications + protocol: HTTP + types: + - org.camaraproject.capability.v0.capability-info-changed + - org.camaraproject.capability.v0.capability-bitmap-changed + config: + subscriptionDetail: + resourceScopes: + - phoneNumber: '+123456788' + CAMARA_CAPABILITY_QUERY_REQUEST_RESPONSE_EXAMPLE: + summary: Example of capability query response + description: query capability response + value: + details: + - name: cap-qod-adi + version: 1.0.1 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 63 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true + '1': + name: rr-qod-xcor + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.parameter-restriction.x-cor-required + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.parameters['x-correlator'] + update: + xcor-required: + restrictions: + - mandatory: true + '2': + name: rr-session-extend-unavailable + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.operation-restriction.session-extend-unavailable + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.paths['/sessions/{sessionId}/extend'].post + update: + session-extend-unavailable: + restrictions: + - notAvailable: true + '3': + name: rr-session-accept-qos + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.enum-restriction.accepted-qos-profiles + version: 0.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + operator: and + actions: + - targetLocations: + - location: $method + update: + accepted-qos-profiles: + restrictions: + - enum: [POST] + - targetLocations: + - location: $request.path.sessionId + update: + accepted-qos-profiles: + restrictions: + - enum: [/sessions] + - targetLocations: + - location: $request.body#/qosProfile + update: + accepted-qos-profiles: + restrictions: + - enum: [QoS_XR, QoS_VC] + '4': + name: rr-ipv6-portspec-max-5 + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.appserv-ipv6 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['ApplicationServer'].properties['ipv4Address'] + remove: true + - name: org.camaraproject.capability.v0.array-size-restriction.portspec-ports-max5 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['PortsSpec'].properties['ports'] + update: + portspec-ports-max5: + restrictions: + - maxItems: 5 + '5': + name: rr-sessioninfo-duration-multipleof-60 + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.numeric-restriction.sessioninfo-duration-min60-multiple60 + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['SessionInfo'].properties['duration'] + update: + sessioninfo-duration-min60-multiple60: + restrictions: + - minimum: 60 + - multipleOf: 60 + '6': + name: rr-qosprofile-get-unavailable + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.operation-restriction.qosprofile-get-unavailable + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + actions: + - target: $.paths['/qos-profiles/{name}'].get + remove: true + EVENT_CAPABILITY_BITMAP_CHANGED_EXAMPLE: + summary: Cloud event example for capability bitmap changed + description: Cloud event example for capability bitmap changed + value: + id: cb1 + source: https://api.example.com/capability/capability-subscriptions/bitmap + datacontenttype: application/json + specversion: '1.0' + type: org.camaraproject.capability.v0.capability-bitmap-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityBitmap: + resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 127 + EVENT_CAPABILITY_BITMAP_CHANGED_BATCH_EXAMPLE: + summary: Batch (single item) - capability bitmap changed + description: Cloud event batch example for capability bitmap changed + value: + - id: cb1 + source: https://api.example.com/capability/capability-subscriptions/bitmap + datacontenttype: application/json + specversion: '1.0' + type: org.camaraproject.capability.v0.capability-bitmap-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityBitmap: + resourceScopes: + - phoneNumber: '+123456788' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 127 + EVENT_CAPABILITY_INFO_CHANGED_EXAMPLE: + description: Cloud event example for capability info changed + value: + id: ci1 + source: https://api.example.com/capability/capability-subscriptions/info + specversion: '1.0' + datacontenttype: application/json + type: org.camaraproject.capability.v0.capability-info-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityInfo: + details: + - name: cap-qod-adi + version: 1.0.2 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 1 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true + EVENT_CAPABILITY_INFO_CHANGED_BATCH_EXAMPLE: + summary: Batch (single item) - capability info changed + description: Cloud event batch example for capability info changed + value: + - id: ci1 + source: https://api.example.com/capability/capability-subscriptions/info + specversion: '1.0' + datacontenttype: application/json + type: org.camaraproject.capability.v0.capability-info-changed + time: '2025-05-06T00:00:00.000Z' + data: + capabilityInfo: + details: + - name: cap-qod-adi + version: 1.0.2 + createdAt: '2025-05-09T14:25:38Z' + overlayExtends: + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + - https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/qos-profiles.yaml + resourceScopes: + - phoneNumber: '+123456788' + mappingVersion: 1.0.0 + camaraCapabilitiesBitmap: 1 + bitmapCapabilities: + '0': + name: rr-qod-adi + version: 1.0.1 + restrictions: + - name: org.camaraproject.capability.v0.object-instance-restriction.accepted-device-identifiers + version: 1.0.1 + extends: https://github.com/camaraproject/QualityOnDemand/blob/r2.2/code/API_definitions/quality-on-demand.yaml + actions: + - target: $.components.schemas['Device'].properties['ipv4Address'] + remove: true + - target: $.components.schemas['Device'].properties['networkAccessIdentifier'] + remove: true diff --git a/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README.MD b/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories.md b/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories.md new file mode 100644 index 0000000000000000000000000000000000000000..93a494556b7967e4c4f50d1604ade3a2c660398d --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/documentation/API_documentation/UserStories.md @@ -0,0 +1,26 @@ + +**User Story: Capabilities and Runtime Restrictions - Query** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want my application to comply with current restrictions applicable based on the service status, network conditions, and location | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Mobile Network Operators (MNO), [Entprerise] Application developers.
                                                      **Scope:** Any device serviced by MNO| +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. Application developer has been onboarded to MNO
                                                      2. MNO offeres Capabilities and Runtime Restrictions APIs
                                                      3. Application developer has subscribed to Capabilities and Runtime Restriction APIs
                                                      4. As necessary, customer consent has been secured
                                                      5. Application developer has implemented Capabilities and Runtime Restriction API
                                                      | +| ***Activities/Steps*** | **Starts when:** Presumably upon mobile application client session start. Application makes a request to retreieve the list of capabilities, their status (enabled/disabled), and restrictions that are applicable to those enabled services, given a particular client.
                                                      **Ends when:** MNO returns the capabilities and runtime restrictions applicable to the request.| +| ***Post-conditions*** |
                                                      1. Application may adjust UI elements according to the current restrictions. The Application, when sending a request to the CAMARA API, can ensure / adjusts information according to the restrictions.
                                                      2. MNO may maintain a cache of the capabilities and restrictions sent in response to Application request.
                                                      | +| ***Exceptions*** | Several exceptions might occur:
                                                      • Unauthorized: Not valid credentials
                                                      • Not found: Client identifier is not managed by the MNO
                                                      • Invalid Input: Request is not properly structured, or missing mandatory input data
                                                      • Service not available: Capabilities and Runtime Restrictions service is [temporarily] not available
                                                      | + +

                                                      + +**User Story: Capabilities and Runtime Restrictions - Subscription** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want my application to comply with current restrictions applicable based on the service status, network conditions, and location. I want my application to subscribe to any changes in capabilities and restrictions | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Mobile Network Operators (MNO), [Entprerise] Application developers.
                                                      **Scope:** Any device serviced by MNO| +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. Application developer has been onboarded to MNO
                                                      2. MNO offeres Capabilities and Runtime Restrictions APIs
                                                      3. Application developer has subscribed to Capabilities and Runtime Restriction APIs
                                                      4. As necessary, customer consent has been secured
                                                      5. Application Client or the Application Backend server has implemented Capabilities and Runtime Restriction API
                                                      | +| ***Activities/Steps*** | **Start when:** Presumably upon mobile application client session start. Application makes a request to receive the current the list of capabilities, their status (enabled/disabled), and restrictions that are applicable to those enabled services and subscribe to any changes after the intial push.
                                                      **Continues with:**
                                                      • Any changes in capabilities or runtime restrictions change sent as an event notification to subscribed Application
                                                      • Application may adjust UI elements according to the current restrictions. The Application, when sending a request to the CAMARA API, can ensure / adjusts information according to the restrictions.
                                                      **Ends when:** Subscrption expires, or subscribing entity terminates the subscription| +| ***Post-conditions*** |
                                                      1. MNO may maintain a cache of the capabilities and restrictions responded with.
                                                      2. Application client may enable/disable UI components based on restricted services at time.
                                                      3. Application client validates, localy or with the Application backend server, Service API prior to making a request to the MNOs Service API endpoint, and avoids any failures.
                                                      | +| ***Exceptions*** | Several exceptions might occur:
                                                      • Unauthorized: Not valid credentials
                                                      • Not found: Client identifier is not managed by the MNO
                                                      • Invalid Input: Request is not properly structured, or missing mandatory input data
                                                      • Service not available: Capabilities and Runtime Restrictions service is [temporarily] not available
                                                      | diff --git a/original/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README.MD b/original/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/CapabilitiesAndRuntimeRestrictions/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/CarrierBillingCheckOut/README.md b/original/CarrierBillingCheckOut/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9957bd1e70779cab244bebf8af5061dd095b10e9 --- /dev/null +++ b/original/CarrierBillingCheckOut/README.md @@ -0,0 +1,58 @@ + + + + + + + + + +# CarrierBillingCheckOut + +Sandbox API Repository to describe, develop, document, and test the CarrierBillingCheckOut Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/CDDe) + +## Scope +* Service APIs for “CarrierBillingCheckOut” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Trigger carrier billing payment request (in one or two steps), which is a process that allows API consumers to make purchases by charging payments against Telco Operator Billing Systems. + * Follow up of payment, by means of query endpoints to get information about a list of payments or a specific payment. + * Trigger carrier billing refund request, which is a process that allows API consumers to ask for a `total` or `partial` return of the amount associated to a previous performed payment. + * Follow up of refund, by means of query endpoints to get information about a list of refunds or a specific refund. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/r3.2) (Fall25), with the following API versions: + * **carrier-billing-refund v0.3.0** + [[YAML]](https://github.com/camaraproject/CarrierBillingCheckOut/blob/r3.2/code/API_definitions/carrier-billing-refund.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing-refund.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing-refund.yaml) + * **carrier-billing v0.5.0** + [[YAML]](https://github.com/camaraproject/CarrierBillingCheckOut/blob/r3.2/code/API_definitions/carrier-billing.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/code/API_definitions/carrier-billing.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CarrierBillingCheckOut/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CarrierBillingCheckOut/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly, Wednesdays 13:00 - 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96513497117?password=ac26d34b-87d2-4d78-aa47-4de1ca14c882) + * Minutes: Access [Meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/CDDe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund.yaml b/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund.yaml new file mode 100644 index 0000000000000000000000000000000000000000..23be6659bea0ef0b4bfc14eab41e0aa13b7e5a22 --- /dev/null +++ b/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing-refund.yaml @@ -0,0 +1,1413 @@ +openapi: 3.0.3 +info: + description: |- + Service Enabling Refunds against Operator Carrier Billing Systems + + # Introduction + + The Carrier Billing Refund API provides programmable interface for developers and other users (capabilities consumers) to perform a refund over a given payment. + The API provides management of a refund entity and its associated lifecycle. + + # Relevant terms and definitions + + - **Carrier Billing**: + An online payment process which allows users to make purchases by charging payments against Telco Operator Billing Systems, accordingly to the user's configuration in the Telco Operator. In a common usage in the industry, the payment is processed on current account balance or charged on next bill generated for this line. + + - **Payment**: + The process of paying for a (set of) good(s)/service(s). + + - **Refund**: + The process of returning the amount involved in a given payment (totally or partially) back to the user. + + # API Functionality + + This API allows to third party clients to request the refund of a given payment, as well as to retrieve information about a specific refund or a list of refunds. + + The API provides several endpoints/operations: + - An endpoint to request a refund, named `createRefund`. + - A set of endpoints to retrieve information about a list of refunds or a specific refund (identified by its specific `refundId`), named `retrieveRefunds` and `retrieveRefund` respectively. + - A callback endpoint where API Server can send notifications about a refund procedure, as defined within `createRefund` operation, towards the `sink` when provided by API client. + - An endpoint to retrieve remaining amount on a payment taken into consideration processed refund, named `retrievePaymentRemainingAmount`. + + State transitions: + + If `createRefund` is a **SYNC** process: + - Response contains `refundId` and refundStatus=`succeeded`. + - In case of any error scenario `refundId` is not created. + + If `createRefund` is an **ASYNC** process: + - Response contains `refundId` and refundStatus=`processing`. After completion: + - When refund is successfully completed then refundStatus=`succeeded`. + - When refund is not successfully performed then refundStatus=`denied`. + - In case of any error scenario `refundId` is not created. That means a `denied` Refund is not considerated as an error for the ASYNC process, because a `denied` Refund is a refund that has been created (i.e. the refund resource exists) and after applying the internal business logic has been settled to `denied` refundStatus. + + # Generic Clarification about optional parameters + + Regarding optional parameters, they can be conditionally mandatory for a Telco Operator to implement them based on business scenarios or applicable regulations in a given market. + + NOTE: Within a given market, in a multi Telco Operator ecosystem, the set of optional parameters to be implemented MUST be aligned among involved Telco Operators. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Carrier Billing Refund + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/CarrierBillingCheckOut +servers: + - url: "{apiRoot}/carrier-billing-refund/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Refund + description: Operations to manage Refund procedure +paths: + /payments/{paymentId}/refunds: + post: + security: + - openId: + - carrier-billing-refund:refunds:create + tags: + - Refund + summary: Create a new Refund + operationId: createRefund + description: Create a new refund for an existing payment. Refund can be `total` or `partial`. This procedure MUST be always limited to the API client which performed the related payment. + parameters: + - name: paymentId + in: path + description: The payment identifier for which the payment refund is requested. + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Refund transaction + content: + application/json: + schema: + $ref: "#/components/schemas/CreateRefund" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Refund Notifications + summary: Carrier Billing refund notifications + operationId: createRefundNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing refund notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Refund" + "400": + $ref: "#/components/responses/RefundInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/RefundPermissionDenied403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/CreateRefundUnprocessableContent422" + "409": + $ref: "#/components/responses/Generic409" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get a list of refunds + operationId: retrieveRefunds + description: |- + Retrieve a list of refunds and their details for a specific payment, identified by its `paymentId`, based on some filtering criteria. + Regardless the refund criteria provided, response MUST be always limited to refunds performed by the API client (i.e same oAuth credentials) triggering this request. + This is to guarantee no API client can check refunds performed by other, therefore avoiding any legal or privacy topic. + + When Access Token is issued for a given user phone number, the list of refunds returned would be only the ones associated to that user phone number and API client. When Access Token is not associated to a user phone number, therefore only associated to API client the list of refunds returned would be all the ones managed by that API client. + + Considerations regarding `refundCreationDate.gte`, `refundCreationDate.lte`: + - If both included, return refunds in that date range + - If no one included, no filtering by date range is applied + - If only settled `refundCreationDate.gte`, `refundCreationDate.lte` is considered current date-time + - If only settled `refundCreationDate.lte`, every refund existing in the Operator billing system until such date is returned + parameters: + - name: paymentId + in: path + description: Payment identifier for which their refunds are queried + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Page" + - $ref: "#/components/parameters/PerPage" + - $ref: "#/components/parameters/StartRefundCreationDate" + - $ref: "#/components/parameters/EndRefundCreationDate" + - $ref: "#/components/parameters/Order" + - $ref: "#/components/parameters/RefundStatus" + - $ref: "#/components/parameters/MerchantIdentifier" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: "#/components/schemas/RefundArray" + "400": + $ref: "#/components/responses/GetRefundsInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/refunds/{refundId}: + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get refund details + operationId: retrieveRefund + description: |- + Retrieve refund details for a given refund. + + When Access Token is issued for a given user phone number, the refund details would be returned in case the `refundId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the refund details are returned in case the API client managed that refund. + parameters: + - name: paymentId + in: path + description: Payment identifier associated to the `refundId` + required: true + schema: + type: string + - name: refundId + in: path + description: Refund identifier that was obtained from the create refund operation + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Refund" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/refunds/remaining-amount: + get: + security: + - openId: + - carrier-billing-refund:refunds:read + tags: + - Refund + summary: Get remaining amount not refunded for a given payment + operationId: retrievePaymentRemainingAmount + description: |- + Retrieve remaining amount not yet refunded for a given payment. This amount refers to the pending amount never requested to be refunded (i.e. a refund not yet consolidated -processing- implies that such an amount is not part of the remaining amount until final status for that procedure is reached). Some cases below to illustrate the behaviour: + + **Case_1:** Payment of 80 EUR, with 2 partial `succedeed` Refunds, each of them of 20 EUR + - remainingAmount: 40 EUR + + **Case_2:** Payment of 80 EUR, with 2 partial Refunds, one `succeeded` of 20 EUR and other `processing` of 15 EUR + - remainingAmount: 45 EUR (API cannot return 60 EUR, because there is an ongoing refund process) + + ***SubCase_A***: Second partial Refund of 15 EUR is `succeeded` + - remainingAmount: 45 EUR + + ***SubCase_B***: Second partial Refund of 15 EUR is `denied` + - remainingAmount: 60 EUR + + **Case_3:** Payment of 80 EUR, with 1 total `succeeded` Refund + - remainingAmount: 0 EUR + + **Case_4:** Payment of 80 EUR, with 1 total `processing` Refund + - remainingAmount: 0 EUR (API cannot return 80 EUR, because there is an ongoing refund process) + + ***SubCase_A***: Total Refund is `succeeded` + - remainingAmount: 0 EUR + + ***SubCase_B***: Total Refund is `denied` + - remainingAmount: 80 EUR + + When Access Token is issued for a given user phone number, information would be returned in case the `paymentId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the information is returned in case the API client managed that payment. + parameters: + - name: paymentId + in: path + description: Payment identifier associated to the `refundId` + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentRemainingAmount" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreateRefund: + type: object + description: Information to create a Refund resource. + required: + - type + properties: + type: + type: string + description: |- + Type of refund. + - `total` stands for a final refund, where whole amount is refunded so as it is not indicated by API Consumer. No more refunds are allowed for that `paymentId`. + - `partial` stands for a partial refund, whose amount is indicated by API Consumer. More refunds are allowed for that `paymentId`. + enum: + - total + - partial + reason: + type: string + description: Reason provided to request the refund. Optionally provided by the user or the merchant. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + discriminator: + propertyName: type + mapping: + total: "#/components/schemas/CreateTotalRefund" + partial: "#/components/schemas/CreatePartialRefund" + CreateTotalRefund: + allOf: + - $ref: "#/components/schemas/CreateRefund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionTotalRefund" + CreatePartialRefund: + allOf: + - $ref: "#/components/schemas/CreateRefund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionPartialRefund" + Refund: + type: object + description: Information about a Refund resource. + required: + - refundId + - refundStatus + - refundCreationDate + - type + properties: + refundId: + type: string + description: Unique Identifier of the refund + example: "AK234rfweSBuWGFUEWFGWEVWRV" + refundStatus: + type: string + description: Specifies the refund status (`processing`, `denied`, `succeeded`). + example: "processing" + type: + type: string + description: |- + Type of refund. + - `total` stands for a final refund, where whole amount is refunded so as it is not indicated by API Consumer. No more refunds are allowed for that `paymentId`. + - `partial` stands for a partial refund, whose amount is indicated by API Consumer. More refunds are allowed for that `paymentId`. + enum: + - total + - partial + refundCreationDate: + type: string + format: date-time + description: Date time when the refund is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + refundDate: + type: string + format: date-time + description: Date time when the refund is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + reason: + type: string + description: Reason provided to request the refund. Optionally provided by the user or the merchant. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + discriminator: + propertyName: type + mapping: + total: "#/components/schemas/TotalRefund" + partial: "#/components/schemas/PartialRefund" + TotalRefund: + allOf: + - $ref: "#/components/schemas/Refund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionTotalRefund" + PartialRefund: + allOf: + - $ref: "#/components/schemas/Refund" + - type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionPartialRefund" + AmountTransactionTotalRefund: + type: object + required: + - refundAmount + - referenceCode + properties: + clientCorrelator: + type: string + description: + Uniquely identifies this create refund request. If there is + a communication failure during the refund request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + refundAmount: + $ref: "#/components/schemas/RefundAmountTotalRefund" + referenceCode: + type: string + description: + Merchant generated refund reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-refund-834tfr2rA3v8r8vr3rv" + RefundAmountTotalRefund: + type: object + description: Information for a `total` refund. Whole amount is refunded so as it is not needed to be provided, then it can be an empty object unless `merchantIdentifier` is indicated. + properties: + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + AmountTransactionPartialRefund: + type: object + required: + - refundAmount + - referenceCode + properties: + clientCorrelator: + type: string + description: + Uniquely identifies this create refund request. If there is + a communication failure during the refund request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + refundAmount: + $ref: "#/components/schemas/RefundAmountPartialRefund" + referenceCode: + type: string + description: + Merchant generated refund reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-refund-834tfr2rA3v8r8vr3rv" + RefundAmountPartialRefund: + type: object + description: Information for a `partial` refund. Amount to be refunded is required. + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + refundDetails: + $ref: "#/components/schemas/RefundDetails" + RefundArray: + description: A list of refund(s) + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Refund" + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. Only `ACCESSTOKEN` is supported so far." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment refund, allowing the client to be notified of any changes during the payment refund's existence. If the token expires while the payment refund is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment refund, allowing the client to be notified of any changes during the payment refund's existence. If the token expires while the payment refund is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + ChargingInformation: + type: object + required: + - amount + - currency + - description + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Amount to be refunded. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingMetaData: + type: object + properties: + merchantIdentifier: + type: string + description: Indicates the merchant identifier. Allows aggregators/partners to specify the actual merchant identifier + example: "eas-12345" + RefundDetails: + type: array + description: Detailed description of the concepts/items considered within a specific refund procedure. + minItems: 1 + items: + $ref: "#/components/schemas/RefundItem" + RefundItem: + type: object + required: + - paymentItemId + - amount + - currency + - description + properties: + paymentItemId: + type: string + description: |- + Unique payment item identifier to which this refund item is related to. Relevant when indicating `refundDetails` to correlate information for a refund regarding this `paymentItemId`. + example: "3goug3uvu32v3b" + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Specific amount to be refunded referred to a specific item. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text referred to a specific item. + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + PaymentRemainingAmount: + type: object + description: Remaining Amount of a given payment not refunded yet. + required: + - amount + - currency + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: Specific amount not yet refunded for the payment. When takes value `0` it means whole payment has been refunded. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text (human readable) to contextualize this amount. Optionally indicated by Telco Operator. + example: "Current Amount not refunded so far" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount refunded by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + CloudEvent: + description: The notification format + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + minLength: 1 + example: "sd5e-uy52-88t4-za66" + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: Type of event as defined in each CAMARA API + minLength: 25 + example: "org.camaraproject.carrier-billing.v0.payment-reserved" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + minLength: 3 + example: "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: "application/json" + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.carrier-billing-refund.v0.refund-completed: "#/components/schemas/EventRefundCompleted" + org.camaraproject.carrier-billing-refund.v0.refund-denied: "#/components/schemas/EventRefundDenied" + org.camaraproject.carrier-billing-refund.v0.refund-in-bill: "#/components/schemas/EventRefundInBill" + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + DateTime: + type: string + format: date-time + description: Timestamp when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-11-03T12:27:10Z" + EventRefundCompleted: + description: Event structure for refund completed + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundCompleted" + EventRefundDenied: + description: Event structure for refund denied + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundDenied" + EventRefundInBill: + description: Event structure for refund in bill (i.e. confirmation about refund will be applied in next bill) + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RefundInBill" + RefundCompleted: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-completed event + - $ref: "#/components/schemas/BasicEvent" + - type: object + required: + - refundDate + properties: + refundDate: + type: string + description: Date when the refund is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + example: "2023-11-03T12:27:08.312Z" + RefundDenied: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-denied event + - $ref: "#/components/schemas/BasicEvent" + - type: object + properties: + denialReason: + type: string + description: Indicates the business reason for denying the refund. + example: "User is blocked due to pending debt" + RefundInBill: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing-refund.v0.refund-in-bill event + - $ref: "#/components/schemas/BasicEvent" + BasicEvent: + type: object + description: Data type to provide basic refund event information + required: + - paymentId + - refundId + - status + - description + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + refundId: + type: string + description: Unique Identifier of the refund + example: "AK234rfweSBuWGFUEWFGWEVWRV" + status: + type: string + enum: + - succeeded + - failed + description: |- + Status of the refund procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + example: "Payment Notification" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Invalid input + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GetRefundsInvalid400: + description: |- + Invalid input. In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Inconsistent refundCreationDate.gte and refundCreationDate.lte values ("code": "CARRIER_BILLING_REFUND.INVALID_DATE_RANGE","message": "Client specified an invalid date range."). + - Request out of range ("code": "OUT_OF_RANGE","message": "Client specified an invalid range."). + - Too many matching records found ("code": "CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS","message": "Too many matching records found. Specify additional/suitable criteria to limit the number of records."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - CARRIER_BILLING_REFUND.INVALID_DATE_RANGE + - CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_DATE_RANGE: + summary: Generic Invalid Date Range + description: Inconsistent refundCreationDate.gte and refundCreationDate.lte values + value: + status: 400 + code: CARRIER_BILLING_REFUND.INVALID_DATE_RANGE + message: "Client specified an invalid date range." + GENERIC_400_OUT_OF_RANGE: + summary: Generic Out Of Range + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_TOO_MANY_MATCHING_RECORDS: + summary: Generic Too Many Matching Records + description: Too many matching records found + value: + status: 400 + code: CARRIER_BILLING_REFUND.TOO_MANY_MATCHING_RECORDS + message: "Too many matching records found. Specify additional/suitable criteria to limit the number of records." + RefundInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - Currency is unknown or not authorized ("code": "INVALID_ARGUMENT","message": "Currency is unknown or not authorized."). + - clientCorrelator still exist ("code": "INVALID_ARGUMENT","message": "clientCorrelator already exist on server."). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_WRONG_CURRENCY: + summary: Generic Wrong Currency + description: Currency is unknown or not authorized + value: + code: INVALID_ARGUMENT + status: 400 + message: "Currency is unknown or not authorized." + GENERIC_400_DUPLICATE_CLIENT_CORRELATOR: + summary: Generic Duplicate Client Correlator + description: clientCorrelator still exist + value: + code: INVALID_ARGUMENT + status: 400 + message: "clientCorrelator already exist on server." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + RefundPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Refund denied by business ("code": "CARRIER_BILLING_REFUND.REFUND_DENIED","message": "Refund denied by business."). + - Payment not eligible for Refund (e.g. Payment conditions agreed do not allow refund) ("code": "CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND","message": "Payment not eligible for refund."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING_REFUND.REFUND_DENIED + - CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_REFUND_DENIED: + summary: Generic Refund Denied + description: Refund denied by business + value: + status: 403 + code: CARRIER_BILLING_REFUND.REFUND_DENIED + message: "Refund denied by business." + GENERIC_403_PAYMENT_NOT_ELIGIBLE_FOR_REFUND: + summary: Generic Payment Not Eligible for Refund + description: Payment not eligible for Refund (e.g. Payment conditions agreed do not allow refund) + value: + status: 403 + code: CARRIER_BILLING_REFUND.PAYMENT_NOT_ELIGIBLE_FOR_REFUND + message: "Payment not eligible for refund." + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + summary: Generic Gone + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateRefundUnprocessableContent422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios considered: + - Unauthorized refund amount requested ("code": "CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT","message": "Unauthorized amount requested."). + - Accumulated threshold refund amount for the user's mobile account overpassed ("code": "CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED","message": "Unauthorized refund request. Accumulated user mobile refunds overpass account amount threshold."). + - Payment is not in suitable status for refund ("code": "CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS","message": "Payment is not yet completed."). + - Property `isTaxIncluded` has not the same value as related Payment ("code": "CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH","message": "Inconsistent isTaxIncluded value with regards to related payment."). + - Refund details provided are inconsistent with regards to the related Payment ("code": "CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH","message": "Inconsistent refundDetails information with regards to related payment."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT + - CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED + - CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS + - CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH + - CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH + examples: + GENERIC_422_UNAUTHORIZED_REFUND_AMOUNT: + summary: Generic Unauthorized Refund Amount + description: Unauthorized refund amount requested + value: + status: 422 + code: CARRIER_BILLING_REFUND.UNAUTHORIZED_AMOUNT + message: "Unauthorized amount requested." + GENERIC_422_GENERIC_422_USER_MOBILE_ACCUMULATED_THRESHOLD_REFUND_AMOUNT_OVERPASSED: + summary: Generic User Mobile Accumulated threshold Refund Amount Overpassed + description: Accumulated threshold refund amount for the user's mobile account overpassed + value: + status: 422 + code: CARRIER_BILLING_REFUND.USER_AMOUNT_THRESHOLD_OVERPASSED + message: "Unauthorized refund request. Accumulated user mobile payments overpass account amount threshold." + GENERIC_422_INVALID_PAYMENT_STATUS: + summary: Generic Invalid Payment Status + description: Payment is not in suitable status for refund + value: + status: 422 + code: CARRIER_BILLING_REFUND.INVALID_PAYMENT_STATUS + message: "Payment is not yet completed." + GENERIC_422_TAXES_MANAGEMENT_MISMATCH: + summary: Generic Taxes Management Mismatch + description: Property `isTaxIncluded` has not the same value as related Payment + value: + status: 422 + code: CARRIER_BILLING_REFUND.TAXES_MANAGEMENT_MISMATCH + message: "Inconsistent isTaxIncluded value with regards to related payment." + GENERIC_422_REFUND_DETAILS_MISMATCH: + summary: Generic Refund Details Mismatch + description: Refund details provided are inconsistent with regards to the related Payment + value: + status: 422 + code: CARRIER_BILLING_REFUND.REFUND_DETAILS_MISMATCH + message: "Inconsistent refundDetails information with regards to related payment." + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + summary: Generic Too Many Requests + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + default: 1 + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + default: 10 + StartRefundCreationDate: + description: Initial `refundCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: refundCreationDate.gte + required: false + schema: + format: date-time + type: string + EndRefundCreationDate: + description: End `refundCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: refundCreationDate.lte + required: false + schema: + format: date-time + type: string + Order: + description: Used to return the sorted results in descending (default) or ascending order, based on `refundCreationDate` property + in: query + name: order + required: false + schema: + default: desc + enum: + - desc + - asc + type: string + RefundStatus: + description: List of refund status to be considered for the query + in: query + name: refundStatus + required: false + schema: + type: array + items: + type: string + enum: + - processing + - denied + - succeeded + MerchantIdentifier: + description: Merchant identifier to filter the results + in: query + name: merchantIdentifier + required: false + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer diff --git a/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing.yaml b/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing.yaml new file mode 100644 index 0000000000000000000000000000000000000000..417d3d04234aa47deb517414c20c95cd64f74b41 --- /dev/null +++ b/original/CarrierBillingCheckOut/code/API_definitions/carrier-billing.yaml @@ -0,0 +1,2289 @@ +openapi: 3.0.3 +info: + description: |- + Service Enabling Payments against Operator Carrier Billing Systems + + # Introduction + + The Carrier Billing API provides programmable interface for developers and other users (capabilities consumers) to charge an amount on a mobile line. + It can be easily integrated and allows end-users to buy digital content in an easy & secured way. The API provides management of a payment entity and its associated lifecycle. + + # Relevant terms and definitions + + - **Carrier Billing**: + An online payment process which allows users to make purchases by charging payments against Telco Operator Billing Systems, accordingly to the user's configuration in the Telco Operator. In a common usage in the industry, the payment is processed on current account balance or charged on next bill generated for this line. + + - **Payment**: + The process of paying for a (set of) good(s)/service(s). + + - **1-STEP Payment**: + Payment process performed in one phase (i.e. one action), that involves all the Telco Operator Carrier Billing Systems checking and trigger the charging request against Billing Systems. + + - **2-STEP Payment**: + Payment process performed in two phases (i.e. two actions). First action deals with payment preparation request to guarantee the reservation of the involved amount. Second action is an explicit confirmation or cancellation of the payment by the user. Any payment not confirmed/cancelled by a given user is discarded after some time in order to avoid inconsistency in the billing systems. + + # API Functionality + + This API allows to third party clients to request the payment of a (set of) digital good(s)/service(s), as well as to retrieve information about a specific payment or a list of payments. + + In the scope of **version v0.5rc1, only one-off payments are covered**. Recurrent payments (a.k.a. payment subscriptions) are not covered so far. + + The API provides several endpoints/operations: + - An endpoint to request a 1-STEP Payment, named `createPayment`. + - A set of endpoints to request a 2-STEP Payment: + - One endpoint to setup the payment reservation, named `preparePayment`. + - A couple of endpoints to confirm/cancel such payment reservation, named `confirmPayment` and `cancelPayment` respectively. + - A set of endpoints to retrieve information about a list of payments or a specific payment (identified by its specific `paymentId`), named `retrievePayments` and `retrievePayment` respectively. + - A callback endpoint where API Server can send notifications about a payment procedure, as defined within `createPayment` and `preparePayment` operations, towards the `sink` when provided by API client. + + The usage of the API is based on Payment resource, which can be created (in 1-STEP or 2-STEP Payment process), confirmed/cancelled (for 2-STEP Payment process), and queried/retrieved (list of payments or a specific payment). + + Before starting to use the API, the developer needs to know about the below specified details: + - **Payment service endpoint**: The URL pointing to the RESTful resource of the payment API. As 1-STEP and 2-STEP processes are managed, 2 separate tags _`One Step Payment`_ and _`Two Step Payment`_ have been defined to explicitly distinguish them in the API specification. A third tag _`Payment`_ is defined for common operations in both processes (query/retrieve list of payments or a specific payment). + - **1-STEP & 2-STEP Payment**: + - **1-STEP Payment**: The request intent is to charge an amount to the mobile line. When the server receives the request, it will check the user account associated with this line and, if nothing prevents it, the amount is charged and will be either bill in next invoice or removed from current line credit/balance. + - **2-STEP Payment**: The first call is to request a payment preparation, which implies an amount reservation. The amount is not charged and the server has to be ready to get a confirmation or a cancellation to perform the payment. Only when the confirmation is done, payment is charged. Depending on business rules of the Telco operator, a `prepared` payment could expire after a defined delay. + - **Notification URL**: Developers may provide a callback URL (`sink` param) on which status change notifications, regarding the payment, can be received from the Telco Operator. This is an optional parameter. + + Following diagram shows the API resources operation sequencing: + ![PaymentSequence](https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/documentation/API_documentation/resources/Carrier_Billing_sequence_diagram.png) + + Follow picture provides information about the payment state engine (state description & transition): + ![Payment State Engine](https://raw.githubusercontent.com/camaraproject/CarrierBillingCheckOut/r3.2/documentation/API_documentation/resources/Carrier_Billing_State_Engine.JPG) + + State transitions: + + **1-STEP Payment** + + If `createPayment` is a **SYNC** process: + - Response contains `paymentId` and paymentStatus=`succeeded`. + - In case of any error scenario `paymentId` is not created. + + If `createPayment` is an **ASYNC** process: + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment is successfully completed then paymentStatus=`succeeded`. + - When payment is not successfully performed then paymentStatus=`denied`. + - In case of any error scenario `paymentId` is not created. + + **2-STEP Payment** + + FIRST STEP + + If `preparePayment` is a **SYNC** process: + - **Case A** - `validationInfo` is NOT provided in response. + - Response contains `paymentId` and paymentStatus=`reserved`. + - **Case B** - `validationInfo` is provided in response. + - Response contains `paymentId` and paymentStatus=`pending_validation`. + - In case of any error scenario `paymentId` is not created. + + If `preparePayment` is an **ASYNC** process: + - **Case A** - `validationInfo` is NOT provided in response. + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment preparation is successfully completed then paymentStatus=`reserved`. + - When payment preparation is not successfully performed then paymentStatus=`denied`. + - **Case B** - `validationInfo` is provided in response. + - Response contains `paymentId` and paymentStatus=`processing`. After completion: + - When payment preparation is successfully completed then paymentStatus=`pending_validation`. [1] + - When payment preparation is not successfully performed then paymentStatus=`denied`. + - In case of any error scenario `paymentId` is not created. + + [OPTIONAL] VALIDATE STEP [1] + + After `validatePayment`, paymentStatus=`reserved` OR `denied`, depending whether it was successful or not. + + SECOND STEP + + After `confirmPayment`, paymentStatus=`succeeded` OR `denied`, depending whether it was successful or not. + + After `cancelPayment`, paymentStatus=`cancelled`. + + # Generic Clarification about optional parameters + + Regarding optional parameters, they can be conditionally mandatory for a Telco Operator to implement them based on business scenarios or applicable regulations in a given market. + + NOTE: Within a given market, in a multi Telco Operator ecosystem, the set of optional parameters to be implemented MUST be aligned among involved Telco Operators. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Carrier Billing + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/CarrierBillingCheckOut +servers: + - url: "{apiRoot}/carrier-billing/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: One Step Payment + description: Operations to manage One Step Payment procedure + - name: Two Step Payment + description: Operations to manage Two Step Payment procedure + - name: Payment + description: Operations to obtain information about payments +paths: + /payments: + post: + security: + - openId: + - carrier-billing:payments:create + tags: + - One Step Payment + summary: Create a new Payment + operationId: createPayment + description: Create a new payment for subsequent charging to an end user. Carrier Billing Server will apply the charging according to business configuration for the end user. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: "#/components/schemas/CreatePayment" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Payment Notifications + summary: Carrier Billing payment notifications + operationId: createPaymentNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing payment notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentCreated" + "400": + $ref: "#/components/responses/PaymentInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentPermissionDenied403" + "404": + $ref: "#/components/responses/IdentifierNotFound404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/PaymentUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + get: + security: + - openId: + - carrier-billing:payments:read + tags: + - Payment + summary: Get a list of payments + operationId: retrievePayments + description: |- + Retrieve a list of payments and their details based on some filtering criteria. + Regardless the payment criteria provided, response MUST be always limited to payments performed by the API client (i.e same oAuth credentials) triggering this request. + This is to guarantee no API client can check payments performed by other, therefore avoiding any legal or privacy topic. + + When Access Token is issued for a given user phone number, the list of payments returned would be only the ones associated to that user phone number and API client. When Access Token is not associated to a user phone number, therefore only associated to API client the list of payments returned would be all the ones managed by that API client. + + Considerations regarding `paymentCreationDate.gte`, `paymentCreationDate.lte`: + - If both included, return payments in that date range + - If no one included, no filtering by date range is applied + - If only settled `paymentCreationDate.gte`, `paymentCreationDate.lte` is considered current date-time + - If only settled `paymentCreationDate.lte`, every payment existing in the Operator billing system until such date is returned + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Page" + - $ref: "#/components/parameters/PerPage" + - $ref: "#/components/parameters/StartPaymentCreationDate" + - $ref: "#/components/parameters/EndPaymentCreationDate" + - $ref: "#/components/parameters/Order" + - $ref: "#/components/parameters/PaymentStatus" + - $ref: "#/components/parameters/MerchantIdentifier" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentArray" + "400": + $ref: "#/components/responses/GetPaymentsInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}: + get: + security: + - openId: + - carrier-billing:payments:read + tags: + - Payment + summary: Get payment details + operationId: retrievePayment + description: |- + Retrieve payment details for a given payment. + + When Access Token is issued for a given user phone number, the payment details would be returned in case the `paymentId` is associated to that user phone number and API client, otherwise `404 NOT_FOUND` will be returned. When Access Token is not associated to a user phone number, the payment details are returned in case the API client managed that payment. + parameters: + - name: paymentId + in: path + description: Payment identifier that was obtained from the create payment operation + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Payment" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + /payments/prepare: + post: + security: + - openId: + - carrier-billing:payments:create + tags: + - Two Step Payment + summary: Prepare (reserve) a payment + operationId: preparePayment + description: Prepare a new payment procedure. Carrier Billing Server will apply the charging according to business configuration for the end user. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: "#/components/schemas/BodyAmountReservationTransactionForReserveInput" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + security: + - {} + - notificationsBearerAuth: [] + tags: + - Payment Notifications + summary: Carrier Billing payment notifications + operationId: preparePaymentNotification + description: | + Important: This endpoint is exposed by the API client, accepting requests in the defined format. + The Carrier Billing server will call this endpoint whenever any carrier billing related event occurs. + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Creates a new carrier billing payment notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BodyAmountReservationTransactionForReserve" + "400": + $ref: "#/components/responses/Payment2StepPrepareInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentPermissionDenied403" + "404": + $ref: "#/components/responses/IdentifierNotFound404" + "409": + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + code: ALREADY_EXISTS + status: 409 + message: "Another session is created for the same UE" + "422": + $ref: "#/components/responses/PaymentUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/validate: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Validate a payment + operationId: validatePayment + description: Validate a given payment with a code, identified by its paymentId. This process is applicable for 2-STEP, when optionally required by business case. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + schema: + type: string + required: true + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Payment Validation + content: + application/json: + schema: + $ref: "#/components/schemas/ValidatePayment" + required: true + responses: + "204": + description: Validation Succeeded + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/ValidatePaymentInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Conflict + description: paymentId already validated + value: + code: ALREADY_EXISTS + status: 409 + message: "Payment already validated" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/confirm: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Confirm a payment + operationId: confirmPayment + description: Confirm a reservation of a given payment, identified by its paymentId. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + schema: + type: string + required: true + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: capture PhoneNumber for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "202": + description: Payment confirmation accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Payment2StepInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentConfirmPermissionDenied403" + "404": + $ref: "#/components/responses/Identifier2StepNotFound404" + "409": + $ref: "#/components/responses/PaymentConfirmConflict409" + "422": + $ref: "#/components/responses/PaymentSecondStepUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" + /payments/{paymentId}/cancel: + post: + security: + - openId: + - carrier-billing:payments:write + tags: + - Two Step Payment + summary: Cancel a payment + operationId: cancelPayment + description: Cancel a reservation of a given payment, identified by its paymentId. + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + required: true + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: capture PhoneNumber for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/PhoneNumber" + required: true + responses: + "202": + description: Payment Cancellation Accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Payment2StepInvalid400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/PaymentCancelPermissionDenied403" + "404": + $ref: "#/components/responses/Identifier2StepNotFound404" + "409": + $ref: "#/components/responses/PaymentCancelConflict409" + "422": + $ref: "#/components/responses/PaymentSecondStepUnprocessable422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CreatePayment: + type: object + required: + - amountTransaction + properties: + amountTransaction: + $ref: "#/components/schemas/AmountTransactionInput" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + PaymentCreated: + type: object + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountTransaction" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + paymentDate: + type: string + format: date-time + description: Date time when the payment is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + PaymentArray: + description: A list of payment(s) + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Payment" + Payment: + type: object + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountTransaction" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + paymentDate: + type: string + format: date-time + description: Date time when the payment is effectively performed. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. Only `ACCESSTOKEN` is supported so far." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment, allowing the client to be notified of any changes during the payment's existence. If the token expires while the payment is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur after the expiration of the requested payment, allowing the client to be notified of any changes during the payment's existence. If the token expires while the payment is still active, the client will stop receiving notifications. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + AmountTransaction: + required: + - phoneNumber + - paymentAmount + - referenceCode + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. Same value as indicated in the request. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForCharge" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. Same value as the one provided in the request. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + example: "urn:payments:AK234rfweSBuWGFUEWFGWEVWRV" + serverReferenceCode: + type: string + description: + Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + example: "ref-pay-834tfr2rA3v8r8vr3rv-serv" + AmountTransactionInput: + type: object + required: + - paymentAmount + - referenceCode + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForCharge" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + PaymentAmountForCharge: + type: object + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + paymentDetails: + $ref: "#/components/schemas/PaymentDetails" + PhoneNumber: + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + ValidatePayment: + type: object + required: + - authorizationId + - code + properties: + authorizationId: + type: string + description: Unique authorization identifier for a specific payment. + example: "Fn34o8g239v3wrb3t" + code: + type: string + description: Code received via SMS to validate and authorize a specific payment, only needed when business case requires it. Sending of this code is outside this specification. + example: "352673" + BodyAmountReservationTransactionForReserve: + required: + - amountTransaction + - paymentId + - paymentStatus + - paymentCreationDate + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + amountTransaction: + $ref: "#/components/schemas/AmountReservationTransactionForReserve" + paymentStatus: + type: string + description: Specifies the payment status (`processing`, `pending_validation`, `denied`, `reserved`, `succeeded`, `cancelled`). + example: "processing" + paymentCreationDate: + type: string + format: date-time + description: Date time when the payment is created in server database. This is a technical information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + validationInfo: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - description: Information to perform otp validation. Only needed when business case requires it. Sending of OTP is outside the scope of this specification. + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + BodyAmountReservationTransactionForReserveInput: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: "#/components/schemas/AmountReservationTransactionForReserveInput" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + allOf: + - description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + - $ref: "#/components/schemas/SinkCredential" + AmountReservationTransactionForReserve: + required: + - phoneNumber + - paymentAmount + - referenceCode + type: object + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: Uniquely identifies this payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. Same value as indicated in the request. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForReserve" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. Same value as the one provided in the request. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + example: "urn:payments:AK234rfweSBuWGFUEWFGWEVWRV" + serverReferenceCode: + type: string + description: + Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + example: "ref-pay-834tfr2rA3v8r8vr3rv-serv" + AmountReservationTransactionForReserveInput: + type: object + required: + - paymentAmount + - referenceCode + properties: + phoneNumber: + type: string + description: |- + Identifies the mobile account to be charged. + + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + + Additional Considerations: + - Take a look to section `# Identifying the phone number from the access token` regarding the use of this field. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+34671999000" + clientCorrelator: + type: string + description: + Uniquely identifies this create payment request. If there is + a communication failure during the payment request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + example: "req-12f2pgh448gh2hvrfrv" + paymentAmount: + $ref: "#/components/schemas/PaymentAmountForReserve" + referenceCode: + type: string + description: + Merchant generated payment reference to uniquely identify the + request, for instance, in the case of disputes. + example: "ref-pay-834tfr2rA3v8r8vr3rv" + PaymentAmountForReserve: + type: object + required: + - chargingInformation + properties: + chargingInformation: + $ref: "#/components/schemas/ChargingInformation" + chargingMetaData: + $ref: "#/components/schemas/ChargingMetaData" + paymentDetails: + $ref: "#/components/schemas/PaymentDetails" + PaymentDetails: + type: array + description: Detailed description of the concepts/items considered within a specific payment procedure. + minItems: 1 + items: + $ref: "#/components/schemas/PaymentItem" + PaymentItem: + type: object + required: + - id + - amount + - currency + - description + properties: + id: + type: string + description: |- + Unique payment item identifier. Relevant to uniquely identify an item within a given payment when `paymentDetails` are provided and also to correlate information when a refund regarding this item is performed, by means of using `refundDetails`. + example: "3goug3uvu32v3b" + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Specific amount to be charged or reserved referred to a specific item. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text referred to a specific item. + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount charged by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingInformation: + type: object + required: + - amount + - currency + - description + properties: + amount: + type: number + format: float + multipleOf: 0.001 + minimum: 0.001 + description: Amount to be charged or reserved. + example: 100 + currency: + type: string + description: Currency code in which amount is expressed as defined in [ISO 4217](https://www.iso.org/iso-4217-currency-codes.html). + example: "EUR" + description: + type: string + description: Description text to be used for information and billing text + example: "FIFA EA Sports 24" + isTaxIncluded: + type: boolean + default: false + description: If true, the `amount` is tax included, if false the `amount` is provided without tax. In both cases, `taxAmount` could be indicated to provide tax amount. + taxAmount: + type: number + format: float + multipleOf: 0.001 + minimum: 0 + description: | + The tax amount charged by the merchant. Indicated when the merchant is the one applying taxes. This field also provides an indicator to the downstream billing system. + example: 21 + ChargingMetaData: + type: object + properties: + merchantName: + type: string + description: Indicates the merchant name. Allows aggregators/partners to specify the actual merchant name + example: "EA Sports" + merchantIdentifier: + type: string + description: Indicates the merchant identifier. Allows aggregators/partners to specify the actual merchant identifier + example: "eas-12345" + fee: + type: number + format: float + multipleOf: 0.01 + description: Percentage of the amount to be received by the requester + example: 10 + purchaseCategoryCode: + type: string + description: A category defining the type of service, product or media being purchased + example: "games" + channel: + type: string + description: The channel over which the requester is interacting with the merchant (e.g. WAP, Web, SMS...) + example: "web" + serviceId: + type: string + description: The identifier of the partner/merchant service being purchased + example: "games-online" + productId: + type: string + description: The product identifier to be combined with the `serviceId` to uniquely identify the product being purchased. For example if the `serviceId` relates to a VOD service, the `productId` can specify the movie rented + example: "138235321" + ValidationInfo: + type: object + required: + - action + properties: + action: + type: string + enum: + - open + - validate + description: Action to be done regarding otp validation. + discriminator: + propertyName: action + mapping: + open: "#/components/schemas/Open" + validate: "#/components/schemas/Validate" + example: + action: validate + authorizationId: "Fn34o8g239v3wrb3t" + Open: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - type: object + description: Information for otp validation by means of browseable URL. + required: + - validationURL + properties: + validationURL: + type: string + description: Backend generated Public URL to perform otp validation. Sending of OTP is outside the scope of this specification. + example: "https://my-payment-service.com/validate/358y24t2g4f2397g45" + Validate: + allOf: + - $ref: "#/components/schemas/ValidationInfo" + - type: object + description: Information for otp validation by means of received otp. + required: + - authorizationId + properties: + authorizationId: + type: string + description: Unique authorization identifier for a given payment to perform otp validation. Sending of OTP is outside the scope of this specification. Validation of this `authorizationId` is performed by means of `validatePayment` endpoint. + example: "Fn34o8g239v3wrb3t" + CloudEvent: + description: The notification format + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + minLength: 1 + example: "sd5e-uy52-88t4-za66" + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: Type of event as defined in each CAMARA API + minLength: 25 + example: "org.camaraproject.carrier-billing.v0.payment-reserved" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + minLength: 3 + example: "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: "application/json" + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.carrier-billing.v0.payment-pending-validation: "#/components/schemas/EventPaymentPendingValidation" + org.camaraproject.carrier-billing.v0.payment-reserved: "#/components/schemas/EventPaymentReserved" + org.camaraproject.carrier-billing.v0.payment-completed: "#/components/schemas/EventPaymentCompleted" + org.camaraproject.carrier-billing.v0.payment-cancelled: "#/components/schemas/EventPaymentCancelled" + org.camaraproject.carrier-billing.v0.payment-denied: "#/components/schemas/EventPaymentDenied" + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + DateTime: + type: string + format: date-time + description: Timestamp when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-11-03T12:27:10Z" + EventPaymentPendingValidation: + description: Event structure for payment pending validation + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentPendingValidation" + EventPaymentReserved: + description: Event structure for payment reserved + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentReserved" + EventPaymentCompleted: + description: Event structure for payment completed + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentCompleted" + EventPaymentCancelled: + description: Event structure for payment cancelled + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentCancelled" + EventPaymentDenied: + description: Event structure for payment denied + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/PaymentDenied" + PaymentPendingValidation: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-pending-validation event + - $ref: "#/components/schemas/BasicEvent" + PaymentReserved: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-reserved event + - $ref: "#/components/schemas/BasicEvent" + PaymentCompleted: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-completed event + - $ref: "#/components/schemas/BasicEvent" + - type: object + required: + - paymentDate + properties: + paymentDate: + type: string + description: Date when the payment is effectively performed, both in 1-step and 2-step scenarios. This is a business information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + example: "2023-11-03T12:27:08.312Z" + PaymentCancelled: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-cancelled event + - $ref: "#/components/schemas/BasicEvent" + PaymentDenied: + allOf: + - description: Event detail structure for org.camaraproject.carrier-billing.v0.payment-denied event + - $ref: "#/components/schemas/BasicEvent" + - type: object + properties: + denialReason: + type: string + description: Indicates the business reason for denying the payment. + example: "User is blocked due to pending debt" + BasicEvent: + type: object + description: Data type to provide basic payment event information + required: + - paymentId + - status + - description + properties: + paymentId: + type: string + description: Unique Identifier of the payment + example: "AK234rfweSBuWGFUEWFGWEVWRV" + status: + type: string + enum: + - succeeded + - failed + description: |- + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + example: "Payment Notification" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GetPaymentsInvalid400: + description: |- + Invalid input. In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Inconsistent paymentCreationDate.gte and paymentCreationDate.lte values ("code": "CARRIER_BILLING.INVALID_DATE_RANGE","message": "Client specified an invalid date range"). + - Request out of range ("code": "OUT_OF_RANGE","message": "Client specified an invalid range"). + - Too many matching records found ("code": "CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS","message": "Too many matching records found. Specify additional/suitable criteria to limit the number of records."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - CARRIER_BILLING.INVALID_DATE_RANGE + - CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_DATE_RANGE: + summary: Generic Invalid Date Range + description: Inconsistent paymentCreationDate.gte and paymentCreationDate.lte values + value: + status: 400 + code: CARRIER_BILLING.INVALID_DATE_RANGE + message: "Client specified an invalid date range." + GENERIC_400_OUT_OF_RANGE: + summary: Generic Out Of Range + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_TOO_MANY_MATCHING_RECORDS: + summary: Generic Too Many Matching Records + description: Too many matching records found + value: + status: 400 + code: CARRIER_BILLING.TOO_MANY_MATCHING_RECORDS + message: "Too many matching records found. Specify additional/suitable criteria to limit the number of records." + PaymentInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - Currency is unknown or not authorized ("code": "INVALID_ARGUMENT","message": "Currency is unknown or not authorized"). + - clientCorrelator still exist ("code": "INVALID_ARGUMENT","message": "clientCorrelator already exist on server"). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_WRONG_CURRENCY: + summary: Generic Wrong Currency + description: Currency is unknown or not authorized + value: + code: INVALID_ARGUMENT + status: 400 + message: "Currency is unknown or not authorized." + GENERIC_400_DUPLICATE_CLIENT_CORRELATOR: + summary: Generic Duplicate Client Correlator + description: clientCorrelator still exist + value: + code: INVALID_ARGUMENT + status: 400 + message: "clientCorrelator already exist on server." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Payment2StepPrepareInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - paymentId is required ("code": "INVALID_ARGUMENT","message": "Expected property is missing: paymentId."). + + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - Invalid sink credential ("code": "INVALID_CREDENTIAL","message": "Only Access token is supported"). + - Invalid sink credential access token ("code": "INVALID_TOKEN","message": "Only bearer token is supported"). + - Invalid sink ("code": "INVALID_SINK","message": "sink not valid for the specified protocol"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_PAYMENT_ID_REQUIRED: + summary: Generic PaymentId required + description: paymentId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: paymentId." + GENERIC_400_INVALID_CREDENTIAL: + summary: Generic Invalid Credential + description: Invalid sink credential + value: + status: 400 + code: "INVALID_CREDENTIAL" + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + summary: Generic Invalid Token + description: Invalid sink credential access token + value: + status: 400 + code: "INVALID_TOKEN" + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + summary: Generic Invalid Sink + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: "sink not valid for the specified protocol" + Payment2StepInvalid400: + description: |- + Invalid input. + Common INVALID_ARGUMENT scenarios usually are: + - Schema validation failed ("code": "INVALID_ARGUMENT","message": "Client specified an invalid argument, request body or query param."). + - paymentId is required ("code": "INVALID_ARGUMENT","message": "Expected property is missing: paymentId."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_PAYMENT_ID_REQUIRED: + summary: Generic PaymentId required + description: paymentId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: paymentId." + ValidatePaymentInvalid400: + description: |- + Invalid input. + In addition to regular INVALID_ARGUMENT scenario other scenarios may exist: + - authorizationId is not valid ("code": "CARRIER_BILLING.INVALID_AUTHORIZATION_ID","message": "Invalid authorizationId."). + - code is not valid ("code": "CARRIER_BILLING.INVALID_CODE","message": "Invalid code."). + - validation failed ("code": "CARRIER_BILLING.VALIDATION_FAILED","message": "the maximum number of attempts have been consumed for this validation."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - CARRIER_BILLING.INVALID_AUTHORIZATION_ID + - CARRIER_BILLING.INVALID_CODE + - CARRIER_BILLING.VALIDATION_FAILED + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Generic Invalid Argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_AUTHORIZATION_ID_REQUIRED: + summary: Generic AuthorizationId Required + description: authorizationId is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: authorizationId." + GENERIC_400_CODE_REQUIRED: + summary: Generic Code Required + description: code is required + value: + code: INVALID_ARGUMENT + status: 400 + message: "Expected property is missing: code." + GENERIC_400_INVALID_AUTHORIZATION_ID: + summary: Generic Invalid Authorization Id + description: authorizationId is not valid + value: + code: CARRIER_BILLING.INVALID_AUTHORIZATION_ID + status: 400 + message: "Invalid authorizationId." + GENERIC_400_INVALID_CODE: + summary: Generic Invalid Code + description: code is not valid + value: + code: CARRIER_BILLING.INVALID_CODE + status: 400 + message: "Invalid code." + GENERIC_400_VALIDATION_FAILED: + summary: Generic Validation Failed + description: validation failed + value: + code: CARRIER_BILLING.VALIDATION_FAILED + status: 400 + message: "the maximum number of attempts have been consumed for this validation." + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + PaymentPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Payment denied by business ("code": "CARRIER_BILLING.PAYMENT_DENIED","message": "Payment denied by business."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING.PAYMENT_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_PAYMENT_DENIED: + summary: Generic Payment Denied + description: Payment denied by business + value: + status: 403 + code: CARRIER_BILLING.PAYMENT_DENIED + message: "Payment denied by business." + PaymentConfirmPermissionDenied403: + description: |- + Client does not have sufficient permission. + In addition to regular PERMISSION_DENIED scenario other scenarios may exist: + - Payment denied by business ("code": "CARRIER_BILLING.PAYMENT_DENIED","message": "Payment denied by business."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CARRIER_BILLING.PAYMENT_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_PAYMENT_DENIED: + summary: Generic Payment Denied + description: Payment denied by business + value: + status: 403 + code: CARRIER_BILLING.PAYMENT_DENIED + message: "Payment denied by business." + PaymentCancelPermissionDenied403: + description: |- + Client does not have sufficient permission. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + IdentifierNotFound404: + description: Phone Number Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Identifier2StepNotFound404: + description: |- + Resource Not Found. + In addition to regular NOT_FOUND scenario other scenarios may exist: + - Phone Number not found ("code": "IDENTIFIER_NOT_FOUND","message": "phoneNumber not found."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + PaymentConfirmConflict409: + description: |- + Conflict. In addition of regular ALREADY_EXISTS scenario other scenarios may exist: + - paymentId is already confirmed ("code": "CARRIER_BILLING.PAYMENT_CONFIRMED","message": "Payment has been confirmed."). + - paymentId is already cancelled ("code": "CARRIER_BILLING.PAYMENT_CANCELLED","message": "Payment has been cancelled."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + - CARRIER_BILLING.PAYMENT_CONFIRMED + - CARRIER_BILLING.PAYMENT_CANCELLED + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_ALREADY_CONFIRMED: + summary: Generic Already Confirmed + description: paymentId is already confirmed + value: + code: CARRIER_BILLING.PAYMENT_CONFIRMED + status: 409 + message: "Payment has been confirmed." + GENERIC_409_ALREADY_CANCELLED: + summary: Generic Already Cancelled + description: paymentId is already cancelled + value: + code: CARRIER_BILLING.PAYMENT_CANCELLED + status: 409 + message: "Payment has been cancelled." + PaymentCancelConflict409: + description: |- + Conflict. In addition of regular ALREADY_EXISTS scenario other scenarios may exist: + - paymentId is already confirmed ("code": "CARRIER_BILLING.PAYMENT_CONFIRMED","message": "Payment has been confirmed."). + - paymentId is already cancelled ("code": "CARRIER_BILLING.PAYMENT_CANCELLED","message": "Payment has been cancelled."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + - CARRIER_BILLING.PAYMENT_CONFIRMED + - CARRIER_BILLING.PAYMENT_CANCELLED + examples: + GENERIC_409_ALREADY_EXISTS: + summary: Generic Already Exists + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_ALREADY_CONFIRMED: + summary: Generic Already Confirmed + description: paymentId is already confirmed + value: + code: CARRIER_BILLING.PAYMENT_CONFIRMED + status: 409 + message: "Payment has been confirmed." + GENERIC_409_ALREADY_CANCELLED: + summary: Generic Already Cancelled + description: paymentId is already cancelled + value: + code: CARRIER_BILLING.PAYMENT_CANCELLED + status: 409 + message: "Payment has been cancelled." + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + summary: Generic Gone + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + PaymentUnprocessable422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios that may exist: + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + - Unauthorized amount requested ("code": "CARRIER_BILLING.UNAUTHORIZED_AMOUNT","message": "Unauthorized amount requested."). + - Accumulated threshold amount for the user's mobile account overpassed ("code": "CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED","message": "Unauthorized payment request. Accumulated user mobile payments overpass account amount threshold."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - CARRIER_BILLING.UNAUTHORIZED_AMOUNT + - CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + GENERIC_422_UNAUTHORIZED_AMOUNT: + summary: Generic Unauthorized Amount + description: Unauthorized amount requested + value: + status: 422 + code: CARRIER_BILLING.UNAUTHORIZED_AMOUNT + message: "Unauthorized amount requested." + GENERIC_422_USER_MOBILE_ACCUMULATED_THRESHOLD_AMOUNT_OVERPASSED: + summary: Generic User Mobile Accumulated threshold Amount Overpassed + description: Accumulated threshold amount for the user's mobile account overpassed + value: + status: 422 + code: CARRIER_BILLING.USER_AMOUNT_THRESHOLD_OVERPASSED + message: "Unauthorized payment request. Accumulated user mobile payments overpass account amount threshold." + PaymentSecondStepUnprocessable422: + description: |- + Client indicates content that is understable by the Server but unable to be processed. + Scenarios that may exist: + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + summary: Generic Too Many Requests + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + default: 1 + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + default: 10 + StartPaymentCreationDate: + description: Initial `paymentCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: paymentCreationDate.gte + required: false + schema: + format: date-time + type: string + EndPaymentCreationDate: + description: End `paymentCreationDate` for running the query. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + in: query + name: paymentCreationDate.lte + required: false + schema: + format: date-time + type: string + Order: + description: Used to return the sorted results in descending (default) or ascending order, based on `paymentCreationDate` property + in: query + name: order + required: false + schema: + default: desc + enum: + - desc + - asc + type: string + PaymentStatus: + description: List of payment status to be considered for the query + in: query + name: paymentStatus + required: false + schema: + type: array + items: + type: string + enum: + - processing + - pending_validation + - denied + - reserved + - succeeded + - cancelled + MerchantIdentifier: + description: Merchant identifier to filter the results + in: query + name: merchantIdentifier + required: false + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap.md b/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap.md new file mode 100644 index 0000000000000000000000000000000000000000..aafb84b91d9297922c02795341b9c672dfb8e240 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing-API-roadmap.md @@ -0,0 +1,14 @@ +# Carrier Billing API roadmap + +**Phase 1 Features - Initial Version** +* Individual Payments Procedure +* Retrieve Details of a Payment Procedure +* OTP Payment validation (2FA SMS OTP) +* (Highly desired) 1-step / 2-step working mode +* (Highly desired) List of Payments Details per Service Provider and Customer (finding a solution to show only the payments performed by such an Service Provider) + +**Phase 2 Features - Future Versions** +* Support for Notifications +* Recurring Payments Procedure +* Refund Payments Procedure +* Features like 3DS secure banking diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API.md b/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API.md new file mode 100644 index 0000000000000000000000000000000000000000..b6ad8d8fd3cc5f28579c4031fb6ab5a8dfa67bea --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/Carrier_Billing_API.md @@ -0,0 +1,251 @@ +# Overview + +The Carrier Billing Payment API provides programmable interface for developers and other users (capabilities consumers) to charge + a digital content purchase or subscription to the mobile line invoice. + +## 1\. Introduction + + +The Carrier Billing Payment API is used by an application to charge an amount on the +mobile line. It can be easily integrated and used through this secured API and +allows end-users to buy digital content in an easy & secured way. The API provides management of a payment entity and its associated lifecycle. + +The carrier billing Payment API is driven from Open Mobile Alliance standard. + + +## 2\. Quick Start + +The usage of the API is based on Payment resource, which can be created (in 1 or 2 steps process), confirmed (for 2-steps process), cancelled (for 2-steps process), queried and retrieved. + + +Before starting to use the API, the developer needs to know about the below specified details: + +**Payment service endpoint** +The URL pointing to the RESTful resource of the payment API. +As we manage 1-step and 2-steps process we have defined 2 separate tags to explicitly +distinct them in the swagger. A third tag 'payment' is defined for common operation for +both process (query & retrieve) + +**Authentication** +Security access keys such as OAuth 2.0 client credentials used by Client applications to invoke the Carrier Billing Payment API. + +**1-Step & 2-Steps** +1-Step process is very simple: The request intent is to charge an amount to the mobile line. When the server receives the request, it will check the user account associated with this line, and, if nothing prevents it, the amount is charged and will be either bill in next invoice or removed from current line credit. + +For 2-steps, the first call is to request a payment preparation. The amount is not charged and the server has to be ready to get a confirmation or a cancellation to perform the payment. Only when the confirmation is done, payment is charged. Depending on business rules of the Telco operator, a 'prepared' payment could expire after a defined delay. + +**Identifier for the mobile line to be charged** +To identify the mobile line to be charged an identifier **must** be provided. This identifier is mapped to the endUserId attribute. + + +**Notification URL** +Developers may provide a callback URL on which status change notifications, regarding the payment, can be received from the service provider. This is an optional parameter. + + + +Sample API invocations are presented in Section 4.6. + +## 3\. Authentication and Authorization + +The Carrier Billing Payment API makes use of the OAUTH 2.0 client credentials grant which is applicable for server to server use cases involving trusted partners +or clients without any protected user data involved. +In this method the API invoker client is registered as a confidential client with an authorization grant type of client_credentials [[1]](#1). + +## 4\. API Documentation + +### 4.1 API Version + +0.7.0 + +### 4.2 Details + +#### 4.2.1 API sequencing + +As described above, the API accommodates 2 distinct processes: one step process (direct request to charge) and two steps process (which requires an intermediate step to confirm/cancel a payment request) + +Following diagram shows the API resources operation sequencing + +
                                                      + +PaymentSequence + +#### 4.2.1 API attributes + + +Attribute definition + +**Payment Class description:** + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| endUserId | Identify the mobile account to be charged - in general mobile number is provided | Mandatory attribute in POST request | +| clientCorrelator | Provided by the requester - Uniquely identifies this create charge request | Optionally valued by requester | +| paymentAmount | See PaymentAmount class table description| Mandatory attribute in POST request | +| referenceCode | Merchant generated payment reference to uniquely identify the request, for example the purchase or order identifier | Mandatory attribute in POST request | +| transactionOperationStatus | Specifies the payment status (example: Processing, Denied, Reserved, Succeeded, Cancelled) | Must be valued by server side (not in POST request) | +| resourceURL | URI of the created resource (same as in the Location header) | Only valued (optionally) by server side (not in POST request) | +| serverReferenceCode | Reference to the charge or refund, provided by the server, and meaningful to the server’s backend system for the purpose of reconciliation | Only valued (optionally) by server side (not in POST request) | +| paymentCreationDate | Date when the payment is created in server data base. This is a technically information | Only valued (optionally) by server side (not in POST request) | +| paymentDate | Date when the payment is effectively performed. This is a business information. | Only valued (optionally) by server side (not in POST request) | +| notificationUrl | Allows asynchronous delivery of purchase related events | Optionally valued by requester - if used, customer needs to have a notification endpoint | +| notificationAuthToken | Authentification token for callback API (if provided) | Optionally valued by requester | + +**PaymentAccount class description:** + +2 classes are defined: + +ChargingInformation: + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| amount | Amount to be charged or reserved (number) | Mandatory attribute in POST request | +| currency | Currency identifier as defined in [ISO4217] | Mandatory attribute in POST request | +| description | Description text to be used for information and billing text | Mandatory attribute in POST request| + + +ChargingMetaData + + **Name** | **Description** | **Comment** | +| -------- | --------- | ----------- | +| onBehalfOf | Allows aggregators/partners to specify the actual payee | Optionally valued by requester | +| purchaseCategoryCode | Allows aggregators/partners to specify the actual payee | Optionally valued by requester | +| channel | Channel where the order occurred | Optionally valued by requester | +| isTaxIncluded | if true, the amount is tax included, if false the amount is provided without tax. In both case, taxAmount could be valued to provide tax amount.| Optionally valued by requester | +| taxAmount | The tax amount charged by the merchant if the charge has tax already included (number). This also provides an indicator to the downstream billing system | Optionally valued by requester | +| serviceId | Identifier of service related to the payment | Optionally valued by requester | +| productId | Identifier of product related to the payment | Optionally valued by requester | + +**Payment State engine** + +Follow schema provides information about the payment state engine (state description & transition) + +PaymentState + + +### 4.3 Endpoint Definitions + +Following table defines API endpoints of exposed REST based for Carrier Billing Payment API management operations. + +| **Endpoint** | **Operation** | **Description** | +| -------- | --------- | ----------- | +| POST
                                                      \/payment/v0/payments | **Create one step payment** | Create request for one step payment | +| POST
                                                      \/payment/v0/payments/prepare | **Create two steps payment** | Create request for two steps payment | +| POST
                                                      \/payment/v0/payments/{paymentId}/confirm | **Confirm a two steps payment** | Confirmation request for a prepared payment | +| POST
                                                      \/payment/v0/payments/{paymentId}/cancel | **Cancel a two steps payment** | Cancellation request for a prepared payment | +| GET
                                                      \/payment/v0/payments | **Query for payment** | Querying for payment(s) with criteria | +| GET
                                                      \/payment/v0/payments/{paymentId} | **Retrieve payment** | Retrieve payment | +
                                                      + +#### Carrier Billing Payment Resource Operations: +
                                                      + +| **Create payment resource (one step)** | +| -------------------------- | +| **HTTP Request**
                                                      POST \/payment/v0/payments
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      endUserId must be provided
                                                      **Request Body Parameters**
                                                      See above table for attribute definition.
                                                      Following attributes are mandatory in the request: endUserId; paymentAmount.chargingInformation.amount; paymentAmount.chargingInformation.currency ; paymentAmount.chargingInformation.description ; referenceCode.
                                                      Following attributes are only valued on server side and not present in POST request: transactionOperationStatus; resourceURL ; serverReferenceCode. + +
                                                      **Response**
                                                      **201: payment created**
                                                      Response body: A complete payment representation as described in above table is provided.
                                                      **400:** **Invalid input.**
                                                      **401:** **Un-authorized.
                                                      **403:** Forbidden.**
                                                      **409:** **Conflict.**
                                                      **500:** **Server Error.**
                                                      **503:** **Service temporarily unavailable.** +
                                                      + + +| **Create payment resource (two steps)** | +| -------------------------- | + **HTTP Request**
                                                      POST \/payment/v0/payments/prepare
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      endUserId must be provided
                                                      **Request Body Parameters**
                                                      See above table for attribute definition. Following attributes are mandatory in the request: endUserId; paymentAmount.chargingInformation.amount; paymentAmount.chargingInformation.currency ; paymentAmount.chargingInformation.description ; referenceCode. Folowing attributes are only valued on server side and not present in POST request: transactionOperationStatus; resourceURL ; serverReferenceCode. + + **Response**
                                                      **201: payment created**
                                                      Response body: A complete payment representation as described in above table is provided.
                                                      **400:** **Invalid input.**
                                                      **401:** **Un-authorized.
                                                      **403:** Forbidden.**
                                                      **409:** **Conflict.**
                                                      **500:** **Server Error.**
                                                      **503:** **Service temporarily unavailable.** +
                                                      + + +| **Confirm payment task (only for two steps process)** | +| -------------------------- | +**HTTP Request**
                                                      POST \/payment/v0/payments/confirm/{paymentId
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      PaymentId must be provided
                                                      **Request Body Parameters**
                                                      endUserId must be provided + + **Response**
                                                      **200: payment confirmation accepted**
                                                      Response body: None

                                                      **400:** **Invalid input.**
                                                      **401:** **Un-authorized.
                                                      **403:** Forbidden.**
                                                      **409:** **Conflict.**
                                                      **500:** **Server Error.**
                                                      **503:** **Service temporarily unavailable.** +
                                                      + +| **Cancel payment task (only for two steps process)** | +| -------------------------- | + **HTTP Request**
                                                      POST \/payment/v0/payments/cancel/{paymentId}
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      endUserId and PaymentId must be provided
                                                      **Request Body Parameters**
                                                      endUserId must be provided + + **Response**
                                                      **202: payment cancellation accepted**
                                                      Response body: None

                                                      **400:** **Invalid input.**
                                                      **401:** **Un-authorized.
                                                      **403:** Forbidden.**
                                                      **409:** **Conflict.**
                                                      **500:** **Server Error.**
                                                      **503:** **Service temporarily unavailable.** +
                                                      + + +#### Query for payment resource + +| **Quering payment Resource /id information** | +| --------------------------------------- | +| **HTTP Request**
                                                      GET\/payment/v0/payments/{paymentId}
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      paymentId: paymentId id that was obtained from the Create payment operation.
                                                      **Request Body Parameters**
                                                      No request body parameters are defined.
                                                      **Response**

                                                      **200: Payment information returned.**
                                                      Response body:
                                                      Complete payment representation as defined in the above table.

                                                      **401:** Un-authorized.
                                                      **403:** Forbidden.
                                                      **404:** Payment not found.
                                                      **503:** Service temporarily unavailable. | +
                                                      + + +| **Quering payment Resource /list information** | +| --------------------------------------- | +| **HTTP Request**
                                                      GET\/payment/v0/payments/{paymentId}
                                                      **Query Parameters**
                                                      No query parameters are defined.
                                                      **Path Parameters**
                                                      endUserId: Identify the mobile account charged - in general mobile number is provided
                                                      fields: Comma-separated attributes to be provided in response
                                                      offset: Requested index for start of resources to be provided in response
                                                      limit: Requested number of resources to be provided in response
                                                      **Request Body Parameters**
                                                      No request body parameters are defined.
                                                      **Response**

                                                      **200: a list of payment(s).**
                                                      Response body:
                                                      An array of payment representation (could be a subset of a complete representation depending on fields filtering).
                                                      Note: It could be empty list if no payment match search criteria.

                                                      **401:** Un-authorized.
                                                      **403:** Forbidden.

                                                      **503:** Service temporarily unavailable. | +
                                                      + +### 4.4 Errors + +Since CAMARA Carrier Billing Payment API is based on REST design principles and blueprints, well defined HTTP status codes and families specified by community are followed [[2]](#2). + +Details of HTTP based error/exception codes for the Carrier Billing Payment API are described in Section 4.3 of each API REST based method. +Following table provides an overview of common error names, codes, and messages applicable to Carrier Billing Payment API. + +| No | Error Name | Error Code | Error Message | +| --- | ---------- | ---------- | ------------- | +|1 |400 | INVALID_INPUT | "Expected property is missing: endUserId" | +|2 |400 | INVALID_INPUT | "Expected property is missing: referenceCode" | +|3 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.amount" | +|4 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.currency" | +|5 |400 | INVALID_INPUT | "Expected property is missing: paymentAmount.chargingInformation.description" | +|6 |400 | INVALID_INPUT | "Expected property is missing: paymentId" | +|7 |400 | INVALID_INPUT | "Expected property is missing: qos" | +|8 |400 | INVALID_INPUT | "Payment status does not allow to confirm it" | +|9 |400 | INVALID_INPUT | "Payment status does not allow to cancel it" | +|10 |401 | UNAUTHORIZED | "No authorization to invoke operation" | +|11 |403 | FORBIDDEN | "Operation not allowed" | +|12 |404 | NOT_FOUND | "Payment Id does not exist" | +|13 |409 | CONFLICT | "Another payment is created for the same client correlator" | +|14 |500 | INTERNAL | "Payment could not be created" | +|15 |503 | SERVICE_UNAVAILABLE | "Service unavailable" | + +### 4.5 Policies + +N/A + +### 4.6 Code Snippets +
                                                      +Snippet 1, elaborates REST based API call with "*curl"* to create a payment for a Video on demand payment + + + +Please note, the credentials for API authentication purposes need to be adjusted based on target security system configuration. + +| Snippet 1. Create Payment resource | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/payment/v0/payments`
                                                      -H 'accept: application/json'
                                                      -H 'Content-Type: application/json'
                                                      -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
                                                      -d '{
                                                      "amountTransaction": {
                                                      "endUserId": "+33068741256+d",
                                                      "paymentAmount": { "chargingInformation": { "amount": 2.99, "currency": "EUR", "description": "VOD charge" },
                                                      "chargingMetaData": {
                                                      "onBehalfOf":"VOD Service",
                                                      "purchaseCategoryCode": "Purchase Movie",
                                                      "channel": "TV",
                                                      "taxAmount": 0.84,
                                                      "isTaxIncluded": true,
                                                      "serviceId": "N/A",
                                                      "productId": "vod-47" }
                                                      },
                                                      "referenceCode": "vod081220225698",
                                                      "clientCorrelator": "78g9-dfg6-fgtr6" },
                                                      "notificationUrl": "https://callback..." | +| response will be:
                                                      201
                                                      -d '{
                                                      "amountTransaction": {
                                                      "endUserId": "+33068741256+d",
                                                      "paymentAmount": { "chargingInformation": { "amount": 2.99, "currency": "EUR", "description": "VOD charge" },
                                                      "chargingMetaData": {
                                                      "onBehalfOf":"VOD Service",
                                                      "purchaseCategoryCode": "Purchase Movie",
                                                      "channel": "TV",
                                                      "taxAmount": 0.84,
                                                      "isTaxIncluded": true,
                                                      "serviceId": "N/A",
                                                      "productId": "vod-47" }
                                                      },
                                                      "referenceCode": "vod081220225698",
                                                      "clientCorrelator": "78g9-dfg6-fgtr6",
                                                      "transactionOperationStatus": "succeeded",
                                                      "resourceURL": "https://localhost:9091/payment/v0/payments/7896321",
                                                      "serverReferenceCode": "7896321" },
                                                      "paymentCreationDate" : "2023-03-10T15:30:58.139Z",
                                                      "paymentDate" : "2023-03-10T15:31:04.139Z",
                                                      "notificationUrl": "https://callback..." }'| +
                                                      + + +### 4.7 FAQ's + +(FAQs will be added in a later version of the documentation) + +### 4.8 Terms + +N/A + +### 4.9 Release Notes + +0.6 Release note +* Added status attribute in Error +* Added attribute notificationAuthToken + +0.7 Release note +* Added paymentCreationDate & PaymentDate +* Added isTaxIncluded flag +## References + + +[1] [CAMARA Commonalities : Authentication and Authorization Concept for Service APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Working/CAMARA-AuthN-AuthZ-Concept.md)
                                                      +
                                                      [2] [HTTP Status codes spec](https://restfulapi.net/http-status-codes/)
                                                      diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist.md b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..4c521b7ad48b6a77f30ab988e2781a1aaf65ccc8 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Carrier Billing v0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Carrier Billing User Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/_oDWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story.md b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..826e298fcffb1e4d1ff17282901993e8f9035668 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-User-Story.md @@ -0,0 +1,52 @@ +**User Story: Make a Payment request in one step** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment (one-time fee -in initial phase- or recurring -in a later phase- ) to be billed against a customer's carrier bill, so that I can offer customers payment alternatives. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Payment on Carrier Bill* \- Initiate Carrier Billing approval process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has Carrier Billing activated as payment method.
                                                      2. The Customer:User has initiated payment via Carrier Billing from application/portal/product channel
                                                      3. The PaymentRequester has verified that associated carrier billing service belongs to the Customer:User (Generally as part of adding a new payment method, 2-Factor-Authorization or equivalent)
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to trigger the payment.
                                                      **Ends when:** The payment is completed and the customer application customer can query details of that payment.
                                                      | +| ***Post-conditions*** | After customer application server performs the payment, payment details can be queried. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Invalid input: Not valid input data to invoke operation (e.g. merchant information not provided or unknown).
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the payment
                                                      • Conflict: Internal configuration policies don't allow for Payment Execution/Cancellation.
                                                      | + + +**User Story: Make a Payment request in two steps** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment (one-time fee -in initial phase- or recurring -in a later phase- ) to be billed against a customer's carrier bill, so that I can offer customers payment alternatives. The payment process will be split in 2 parts:
                                                      1. Payment preparation request (that did not trigger the payment but only prepare it)
                                                      2. Payment confirmation or cancellation. The payment confirmation triggers the payment itself. Optionally, as per business needs, payment confirmation may require a payment validation in advance (i.e. an optional step between payment preparation and payment confirmation)
                                                      | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Payment on Carrier Bill* \- Initiate Carrier Billing 2-steps approval process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has Carrier Billing activated as payment method.
                                                      2. The Customer:User has initiated 2-steps payment via Carrier Billing from application/portal/product channel
                                                      3. The PaymentRequester has verified that associated carrier service belongs to the Customer:User (Generally as part of adding a new payment method, 2FA or equivalent)
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to trigger a 2-steps payment.
                                                      **Intermediate steps:** The customer application server makes a request to confirm or cancel the payment preparation
                                                      **Ends when:** If payment confirmation is provided the payment is completed. If a payment cancellation is provided (explicit cancellation) or if neither a confirmation or cancellation is received after a predefined business delay (implicitly by expiration), the payment preparation is cancelled.
                                                      For both cases the customer application can retrieve and/or query details of that payment
                                                      | +| ***Post-conditions*** | After customer application server performs the payment, payment details can be queried. A payment can stay in preparation status only for a predefined business delay. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Invalid input: Not valid input data to invoke operation like for example:
                                                        merchant information not provided or unknown,
                                                        payment identifier not existing or not linked to the customer:user,
                                                        payment confirmation for an expired payment,
                                                        payment cancellation request for an already confirmed payment).
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the payment. Payment preparation as payment confirmation could be denied
                                                      • Conflict: Internal configuration policies don't allow for Payment Execution/Cancellation.
                                                      | + + +**User Story: Retrieve a Payment from its identifier** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get details of one performed payment (from its id) by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Payments Details done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has performed payments via application, both success and failed
                                                      2. The Customer:User has payment identification.
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to get payments details performed via that application providing payment identifier.
                                                      **Ends when:** Response is received from Carrier Billing service showing the payment details | +| ***Post-conditions*** | Requester receives a complete representation of the payment. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Invalid input: Not valid payment identifier to invoke operation.
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the payment
                                                      | + + +**User Story: Retrieve a Payment list** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get a list of performed payments from criteria (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Payments list done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has performed payments via application, both success and failed
                                                      2. The requester provides a list of criteria(s) to select payment (Customer/user identifier, payment status)
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing service (API) to get payment/payments details performed via that application
                                                      **Ends when:** Response is received from Carrier Billing service showing the details | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the payment
                                                      | + +
                                                      diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist.md b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..cde05f793a90191a4f8af13ed70b02be5e9dd244 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Carrier Billing Refund v0.3.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing-refund.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/carrier-billing-refund.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Carrier Billing Refund User Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYBSBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story.md b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..d149039e0da4ce54d10ebfd728b8ab70057f0ce1 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/API_documentation/carrier-billing-refund-User-Story.md @@ -0,0 +1,52 @@ +**User Story: Make a Payment Refund request in one step** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) a payment refund (_total_: requesting whole payment amount or whole remaining payment amount not yet refunded, so as no more refunds can be requested; or _partial_: requesting a specific payment amount refund less than the overall amount related to the payment done, so as in principle more refunds can be requested, until performing a total refund or not having remaining payment amount to be refunded) to be billed against a customer's carrier bill. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Refund on Carrier Bill* \- Initiate Carrier Billing Refund process with Customer from Carrier Channels (SMS/App) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has Carrier Billing activated as payment method.
                                                      2. The Customer:User has initiated Refund via Carrier Billing from application/portal/product channel
                                                      3. The RefundRequester has verified that associated carrier billing service belongs to the Customer:User (Generally as part of adding a new payment method, 2-Factor-Authorization or equivalent)
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to trigger the refund.
                                                      **Ends when:** The refund is completed and the customer application customer can query details of that refund.
                                                      | +| ***Post-conditions*** | After customer application server performs the refund, refund details can be queried. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Invalid input: Not valid input data to invoke operation (e.g. invalid paymentId).
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the perform of the refund
                                                      • Conflict: Internal configuration policies don't allow for Refund Execution.
                                                      | + + +**User Story: Retrieve a Payment Refund from its identifier** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get details of one performed refund (from its id) by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Refund Details done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has performed refunds via application, both success and failed
                                                      2. The Customer:User has payment identification and refund identification.
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get refund details performed via that application providing payment identifier and refund identifier.
                                                      **Ends when:** Response is received from Carrier Billing Refund service showing the refund details | +| ***Post-conditions*** | Requester receives a complete representation of the refund. | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Invalid input: Not valid payment identifier or refund identifier to invoke operation.
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the refund
                                                      | + + +**User Story: Retrieve a Payment Refunds list** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get a list of performed refunds, for a given payment, from criteria (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Refunds list done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has performed refunds via application, both success and failed
                                                      2. The requester provides a list of criteria(s) to select refund (Customer/user identifier, refund status)
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get refund/refunds details performed via that application
                                                      **Ends when:** Response is received from Carrier Billing Refund service showing the details | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                      • Denied by Carrier: Any user/business condition and/or regulation that forbids the retrieval of the refund
                                                      | + + +**User Story: Retrieve a Payment Amount Not Refunded yet** +
                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to get the remaining amount not yet refunded for a given payment (using my application server/backend service), by means of that application. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                      **Scope:** *Request Remaining Amount not yet refunded done against Carrier Billing* | +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The Customer:User has performed refunds via application, both success and failed
                                                      2. The requester provides payment identification
                                                      | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the Carrier Billing Refund service (API) to get the remaining amount not yet refunded for a given paymentId performed via that application
                                                      **Ends when:** Response is received from Carrier Billing Refund service showing the remaining amount not yet refunded | +| ***Post-conditions*** | N/A | +| ***Exceptions*** | Several exceptions might occur during the Carrier Billing Refund API operations:
                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token). | + +
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07.md new file mode 100644 index 0000000000000000000000000000000000000000..c056788f9ffc25d34a6121841e29f5198330f196 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-06-07.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-jun-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Jan Friman (ERICSSON) +- Rittwik Jana (GOOGLE) +- Masaharu Hattori (KDDI) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG (ORA,TEF) | Decision in CAMARA API for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +New Participants | Welcome to Rittwik, Masa and Jim. Explained the current situation within the CAMARA Carrier Billing WG +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Telefonica introduces rationale and history behind the Issue. Current status is trying to reach an agreement and not wait for a vote that can be delayed in time.
                                                        • Therefore, after internal checking, Telefonica is OK to consider Orange proposal under certain conditions. Points under consideration are listed in this [PowerPoint Slide](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/CarrierBilling_AgreementProposal_20230607.pptx).
                                                        • Orange has initially agreed in these conditions.
                                                        • Based on this initial agreement, Telefonica & Orange will work to integrate all these points in a common contribution. We are open to comment/issue from the team.
                                                        • Good feedback from the team waiting to receive that common input (Ericsson, STC).
                                                        • Google asks if there is currently an API for this WG. Orange indicates there is not yet, there are two proposals and Orange and Telefona are working on presenting a common proposal based on agreement guidelines.
                                                        • Telefonica indicates hopefully to have an initial common proposal soon because wants to promote Carrier Billing API in an MVP this year. If needed, ad-hoc meeting can be scheduled to present&discuss proposal. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09.md new file mode 100644 index 0000000000000000000000000000000000000000..2aa5646efe625089fb75f67caf7d6c2cb5c81912 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-09.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 09-nov-2022
                                                        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Albaraa Bajnaid (STC) +- Pedro Díez (Telefonica) + +## Goals +Attendees presentation
                                                        +Initial aligment on features
                                                        +Initial point of view of participants + +Item | Who | Description +---- | ---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Telefonica | Initial API Proposal + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | Two User Stories defined, one related to Payment procedure and the other one related to Payment Method Provisioning/Onboarding. About the first one, there are no relevant comments and participants are aligned about it. Regarding the second one, STC comments about some business scenarios (Apple), in which payment method provisioning is needed. On this matter, Orange and Telefonica provide comments in the line that this functionality is not really part of "core" payment functionalty, so this functionality maybe fits in later version or other CAMARA track. +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | A first set of features are commented to check participants view on them:
                                                        **Individual Purchase/Payment**:
                                                        • Orange: Model is splitted and purchase and payment are 2 distinct entities (with of course relationship. They have their own lifecycle. From Orange perspective, priority is payment. Individual Payment is first priority.
                                                        • STC: Individual Payment is also first priority.
                                                        • Telefonica: Analogous comment, this feature is first priority
                                                        **Recurrent Purchase/Payment (a.k.a. subscriptions)**: All participants agree on having this feature as a second priority
                                                        **OTP Payment validation (2FA SMS OTP)**: All participants have the same view on considering this feature as first priority.
                                                        • STC also indicates the need to deal with scenarios managed not only by SMS OTP but also via Push Notifications
                                                        **Retrieve Purchase/Payment Details**: All participants agree on having payment details as a first priority feature. Also list of payments is commented as a valuable feature.
                                                        • In baseline proposal not included the list feature by Telefonica due to the fact of managing payment list between different Apps (scenario: one App cannot see payments performed by other App and viceversa)
                                                        **Refund**: All participants share the view of having this feature as a second priority
                                                        NOTE: Orange indicates within this issue the consideration of having 1/2-STEP payment flow approach (i.e. having both options at OBs discretion). [Reference Flow](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/Carrier%20Billing%20sequence%20diagram.png) +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Initial API Proposal.
                                                        • Telefonica introduces the initial proposal, indicating the concepts of Purchase and Payments, the 2-step process (prepare and confirm/cancel) and the asynchronous option behaviour -via notifications_uri-).
                                                        Orange provides two comments over it:
                                                        • Purchase / Payment model splitted (relationship between both concepts are done by reference: an order could refer a payment, then the comment about focusing on Payment withing this track).
                                                        • Use of notifications seen technically as a good approach, however experience observed with end developers indicates more frequent the use of polling. So proposing to have notifications in a latter phase.
                                                        • STC asks about OTP validation procedure, how it works. Telefonica indicates initially thinking in a process embbebed within Payment Preparation Phase (managed internally by OB systems, that generate an SMS towards authorized msisdn and provide info in response to present OTP validation link.
                                                        As part of this issue discussion, Orange comments about having a view about payment status and available transactions between them. + +### Next Steps +- Agree on first proposal features scope @PedroDiez initiates issue +- Work on Payment status and transitions @PedroDiez initiates issue +- Think about options for OTP validation (in 1-STEP scenario as well in order to figure out) @all diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16.md new file mode 100644 index 0000000000000000000000000000000000000000..8dc4040231a57e1b3bbcb34ad47c33ad3d3249f3 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-16.md @@ -0,0 +1,42 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 16-nov-2022
                                                        +**Status:** FINAL + +## Attendees +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Mohammed Nayeenuddin (STC) +- Mohammed Amir (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
                                                        +Aligment on features - first phase
                                                        +Inform about merging of initial draft in this week +Inform about having first stable API version by 28/30 Nov. + + +Item | Who | Description +---- | ---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Telefonica | Initial API Proposal + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | Agreed User Story defined related to Payment procedure. Pending Details to be completed. New one about Obtain Payment(s) Details should be added. +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Features grouping in phases talked in the meeting. Orange and Telefonica OK with that grouping. STC to provide feedback by tomorrow (17/11). +[Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) | Initial API Proposal.
                                                        • Telefonica comments CAMARA Steerco guideline to have draft proposal by 18/11. Proposes to merge initial v0.1.0 with Disclaimer is draft proposal, because there are points to be still analyzed/discussed. Will wait for STC tomorrow feedback to make initial adjustments prior to merge
                                                        • **Purchase/Payment**: Telefonica comments its proposal is to keep purchase concept and Orange comments do not see purchase concept in the model. So OPEN point for further discussion. Orange also indicates in the meeting it will provide a swagger contribution without purchase concept to help understanding of this different approach. Provided after the meeting in [Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16)
                                                        • **1-step/2-step**: Up to OBs discretion, both would be allowed. 1-STEP: payment performed in 1 interaction (confirm-execute). 2-STEP: payment performed in 2 interactions (prepare/confirm-execute). CancelPayment procedure only applies in a 2-STEP model. [Reference Flow](https://github.com/camaraproject/CarrierBillingCheckOut/blob/main/documentation/SupportingDocuments/Carrier%20Billing%20sequence%20diagram.png)
                                                        • **otp_validation**: In 1-step, initially would fit into procedure response. In 2-step, it would apply in preparePayment response. Better to see in a flow.
                                                        • **User identification**. Raised by STC in order to provide MSISDN. Telefonica explains Use Case is Mobile access so OB Mobile IP authentication features would identify MSISDN subscription. Then that can be associated (outside API scope) to Authorization issued, so MSISDN is not really required to be indicated. Orange shares STC concern about the issue 3 as they have scenario where the API requester could be another party and then a MSISDN or an end user id must be available in the request. +[Issue 15 - Carrier Billing Checkout Status](https://github.com/camaraproject/CarrierBillingCheckOut/issues/15) Explained during the meeting. To be checked by participants offline + +### Next Steps +- After the meeting closed informative issues: +[Issue 12 - Adding Diagram to show 1-STEP, 2-STEP Model] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/12) +[Issue 13 - MoM 09/NOV available](https://github.com/camaraproject/CarrierBillingCheckOut/issues/13) +- Check by participants offline Issue 15 documentation +- Improve User Stories. Add the one about Payment Details +- [Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3) Update initial proposal for initial v0.1.0 draft merge after feedback by STC of issue 10. Also update diagrams diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23.md new file mode 100644 index 0000000000000000000000000000000000000000..ded101aba2308351d75c7c1e6db665f50bcf7994 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-11-23.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 23-nov-2022
                                                        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Udaka Kappagoda (Dialog Axiata) +- Ushan Kanahitiyanage (Dialog Axiata) +- Robert Ludovic (Orange) +- Sylvain Morel (Orange) +- Albaraa Bajnaid (STC) +- Mohammed Nayeenuddin (STC) +- Mohammed Amir (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
                                                        +Review Orange's contribution + + +Item | Who | Description +---- | ---- | ---- +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16) | Orange | Orange Contribution for Carrier Billing + + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Based on that issue, a PR is generated. [Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18). Kind request to be reviewed by the WG team (some reviewers added) for approval, in order to be merged. Expected for this week. +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC updates PR during the week to gather first two scenarios. Kind request to be reviewed by the WG team for approval, in order to be merged. Expected for this week. +[Pull Request 16](https://github.com/camaraproject/CarrierBillingCheckOut/pull/16) | Orange explains its proposal for Carrier Billing. Before initiating explanation Telefonica comments about discussion thread in git:
                                                        • Telefonica proposal do not include some cases (invoices) as no Use Case so far. Regarding differents payments (for items) for one purchase, in the same fashion. Orange clarifies just making some payments for the items included in a payment.

                                                        Orange explains its proposal baseline: Proposal OMA-based, explaining they see a model following OMA body structures guidelines, maybe adding/removing some params to be aligned with Use Cases and provide a simpler interface as possible. Input structures for 1-STEP/2-STEP initiation procedures are analogous, provides initial explanation about semantic of params. Maybe responses could be simplified. Some comments around some params raised from STC (tax_amount, channel) and Telefonica (conceptualization of items in model). PurchaseId could be included as an addition of OMA-based input.
                                                        Situation: This proposal has a different approach with regards to Telefonica one [Issue 3](https://github.com/camaraproject/CarrierBillingCheckOut/issues/3), whose baseline is [Pull Request 4](https://github.com/camaraproject/CarrierBillingCheckOut/pull/4). Orange sees Purchase/Payment as different business concepts whilst Telefonica considers Purchase as the object that models the concept to be paid and the payment the action of charging for it. Telefonica needs to check internally this approach in order to provide feedback and comment if it can be accepted. + + +### Next Steps +- After the meeting closed informative issues: +[Issue 17 - MoM 16/NOV available](https://github.com/camaraproject/CarrierBillingCheckOut/issues/17) +- Telefonica will comment about Orange proposal +- Next meeting 30/NOV diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01.md new file mode 100644 index 0000000000000000000000000000000000000000..e945d0ac63a63431bfa02f333939361a2133f060 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-01.md @@ -0,0 +1,40 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 01-dec-2022
                                                        +**Status:** FINAL + +## Attendees +- Vaishali Gupta (Dell Technologies) +- Gareth Williams (GSMA) +- Ludovic Robert (Orange) +- Nayeenuddin Mohammed (STC) +- Amir Mohammed (STC) +- Pedro Díez (Telefonica) + +## Goals +Review Issues
                                                        +Inform about status in WG + + +Item | Who | Description +---- | ---- | ---- +[Issue 20](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | Telefonica | MoM 23/NOV +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | Telefonica | Features discussion +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | STC | Initial User Stories +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | WG | Open Contributions to WG + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 20](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | MoM available in [Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19). Agreed but cannot be merged after activation of merging rules. Ludovic (Orange) kindly offers to be codeowner. Requested in [Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) +[Issue 10](https://github.com/camaraproject/CarrierBillingCheckOut/issues/10) | PR content is agreed [Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18). Pending to be approved to be merged. +[Pull Request 7](https://github.com/camaraproject/CarrierBillingCheckOut/pull/7) | CLOSED. Agreed initial input from STC and merged after the meeting.
                                                        • Orange proposes to generate 4 User Stories (User Stories for 1-STEP and 2-STEP procedures and User Stories for Retrieve Details of a Payment and List Payments based in some criteria).
                                                        • Accepted in the meeting and Orange will make proposal +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/20) | Opened to reflect current status of two different proposals presented by Telefonica and Orange that cannot be accepted each other. Commented in the meeting that this issue is open to provide free opinion from other participants about any preference. Tomorrow it will be a call to discuss about rules/procedures regading this type of situations. Waiting to have guidance to move forward. Some discussion around this:
                                                        • STC asks about how to deal with OTP in proposal from Orange and the need of merchant information to be mandatory.
                                                        • Orange comments that merchant information can be accomodated and regarding OTP validation they see as a separate functionality implemented via a MC-based solution.
                                                        • Telefonica indicates in its proposal OTP validation is internally triggered as Backend Logic (generating SMS towards user) and API returns URL where OTP can be validated. + + +### Next Steps +- Approval of Pull Request 22 to deal with weekly activities within WG (needed at least two "operative" codeowners) +- Approval of Pull Requests 18 and 19 +- Next meeting 07/DEC diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07.md new file mode 100644 index 0000000000000000000000000000000000000000..a03bb0afc6b4f818c62f52299a3fd5c2cf82a3ab --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-07.md @@ -0,0 +1,55 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-dec-2022
                                                        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Ludovic Robert (Orange) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG
                                                        +Inform about progress of Issues/PRs +Next Steps + + +Item | Who | Description +---- | ---- | ---- +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | WG | Open Contributions to WG +[Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) | WG | Adding Ludovic as codeowner +[Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18) | Telefonica | Roadmap Of features +[Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19) | Telefonica | MoM 23/NOV +[Pull Request 23](https://github.com/camaraproject/CarrierBillingCheckOut/pull/23) | Telefonica | MoM 23/NOV +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | Orange | User Story update + payment state engine +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | Orange | Carrier Billing Payment Proposal v0.5 +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | Telefonica | Carrier Billing Checkout Proposal v0.5 + + +### Items Discussion + +Item | Discussion +---- | ---- + +[Issue 21](https://github.com/camaraproject/CarrierBillingCheckOut/issues/21) | As per output of 02/DEC meeting, proposals from Orange and Telefonica will be part of Carrier Billing family APIs. Keep this issue opened to track alignment of relevant actions to fullfil documentation for both. Target to have APIs documentation is 16th December.
                                                        +[Pull Request 22](https://github.com/camaraproject/CarrierBillingCheckOut/pull/22) | New codeowner added (Ludovic), given acceptance from Markus. This will allow WG to progress in main work in the short term.
                                                        +[Pull Request 18](https://github.com/camaraproject/CarrierBillingCheckOut/pull/18) | Roadmap of features. MERGED. CLOSED related Issue 10.
                                                        +[Pull Request 19](https://github.com/camaraproject/CarrierBillingCheckOut/pull/19) | MoM 23/NOV. MERGED. CLOSED related Issue 20.
                                                        +[Pull Request 23](https://github.com/camaraproject/CarrierBillingCheckOut/pull/23) | MoM 01/DEC. MERGED.
                                                        +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | User Story update + payment state engine.
                                                        • Orange explains the rationale of the proposal and the separation in 4 US. Additionaly, it provides a Payment state machine.
                                                        • Telefonica understands Payment state model, same statuses although with some different names. Will review contribution offline
                                                        • STC will review offline this contribution.
                                                        ALL, review contribution and provide comments/give OK.
                                                        +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | To be merged after meeting. If anyone has doubts/comments, it may be provided offline.
                                                        +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | To be merged after meeting. If anyone has doubts/comments, it may be provided offline.
                                                        + + +### Next Steps +- Documentation required: + - API readiness Checklist. Telefonica to update filename to remove "Checkout" + - User Stories. To have it completed Pull Request 25 is pending to be merged + - API Proposals yaml. Ongoing with Pull Requests 26 and 27 to be merged after the meeting + - Full API documentation. See next point +- Elaborate full documentation for both proposals (Orange/Telefonica). [Points](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-DocumentationTemplate.md) to be covered. [Example reference](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoD_API.md) +- APs: @PedroDiez + - Once APIs Proposals are merged, generate PR to remove old ones. + - Review and Update naming of some documents (removing wording checkout, as are common to APIs family) +- Next meeting 14/DEC diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14.md new file mode 100644 index 0000000000000000000000000000000000000000..5a2572130f1813254639746c8e4facdee4dc8324 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-14.md @@ -0,0 +1,53 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 14-dec-2022
                                                        +**Status:** FINAL + +## Attendees +- Ludovic Robert (Orange) +- Aamir Aftab Muhammad (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG
                                                        +Inform about progress of Documentation/PRs +Next Steps + + +Item | Who | Description +---- | ---- | ---- +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | Orange | User Story update + payment state engine +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | Orange | Carrier Billing Payment Proposal v0.5 +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | Telefonica | Carrier Billing Checkout Proposal v0.5 +[Pull Request 28](https://github.com/camaraproject/CarrierBillingCheckOut/pull/28) | WG | MoM 07-DEC +[Pull Request 29](https://github.com/camaraproject/CarrierBillingCheckOut/pull/29) | Telefonica | Rename documentation files +[Pull Request 30](https://github.com/camaraproject/CarrierBillingCheckOut/pull/30) | Telefonica | Remove old files +[Pull Request 31](https://github.com/camaraproject/CarrierBillingCheckOut/pull/31) | Telefonica | User Stories format +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Orange | Carrier Billing Payment API documentation + Yaml update + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 25](https://github.com/camaraproject/CarrierBillingCheckOut/pull/25) | CLOSED. Merged after meeting
                                                        +[Pull Request 26](https://github.com/camaraproject/CarrierBillingCheckOut/pull/26) | CLOSED. Merged after meeting
                                                        +[Pull Request 27](https://github.com/camaraproject/CarrierBillingCheckOut/pull/27) | CLOSED. Merged after meeting
                                                        +[Pull Request 28](https://github.com/camaraproject/CarrierBillingCheckOut/pull/28) | WG | MoM 07-DEC. Pending approval
                                                        +[Pull Request 29](https://github.com/camaraproject/CarrierBillingCheckOut/pull/29) | CLOSED. Merged during week. Rename some documentation files to take off "checkout" wording and be generic for Carrier Billing APIs family
                                                        +[Pull Request 30](https://github.com/camaraproject/CarrierBillingCheckOut/pull/30) | CLOSED. Merged during week. Remove old contribution files for folder clean-up.
                                                        +[Pull Request 31](https://github.com/camaraproject/CarrierBillingCheckOut/pull/31) | CLOSED. Merged during week. Fixing some format of the User Stories file.
                                                        +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Carrier Billing Payment API documentation + Yaml update. API Documentation for Carrier Billing Payment Proposal.
                                                        To be reviewed by Team. Telefonica comments it will provide its proposal documentation by 15/DEC.
                                                        STC comments about how to manage OTP validation in this proposal. Orange indicates they see as a separate functionality that can be manged by other means. Also STC comments about consent management and Orange and Telefonica indicates that track is part of Commonalities WG. + + +### Next Steps +- Documentation required: + - Full API documentation. Target is 19/DEC + - On 15/DEC contributors completed/merged their proposals:
                                                        + - Orange Contribution [Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) + - Orange - Minor Update in Payment State Engine Picture [Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) + - Telefonica Contribution [Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) + +- Next meeting 19/DEC. Short meeting. diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21.md new file mode 100644 index 0000000000000000000000000000000000000000..fbb44a10a244037bde8ec7687ef222ba235743c8 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2022-12-21.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-dec-2022
                                                        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Aamir Aftab Muhammad (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (Telefonica) + +## Goals +Review status of the WG: Proposals yaml and documentation provided
                                                        +Next Meetings schedule + +Item | Who | Description +---- | ---- | ---- +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Orange | Carrier Billing Payment API documentation + Yaml update +[Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) | Telefonica | Carrier Billing Checkout API documentation + Yaml update +[Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) | Orange | Update in Payment State Engine Picture + + +### Items Discussion + +Item | Discussion +---- | ---- +[Pull Request 32](https://github.com/camaraproject/CarrierBillingCheckOut/pull/32) | Carrier Billing Payment API documentation + Yaml update. CLOSED. Merged on 18/DEC. +[Pull Request 33](https://github.com/camaraproject/CarrierBillingCheckOut/pull/33) | Carrier Billing Checkout API documentation + Yaml update. CLOSED. Merged on 18/DEC +[Pull Request 37](https://github.com/camaraproject/CarrierBillingCheckOut/pull/37) | Update in Payment State Engine Picture. CLOSED. Merged on 18/DEC +WG Status | Documentation and yaml of both proposals is available.
                                                        • [APIs Documentation](https://github.com/camaraproject/CarrierBillingCheckOut/tree/main/documentation/API_documentation)
                                                        • [YAMLs](https://github.com/camaraproject/CarrierBillingCheckOut/tree/main/code/API_definitions)
                                                        Telefonica indicates if there is any comment regarding its proposal. STC comments that will review proposal offline and provide comments/doubts. +Meetings Schedule | Mainly talked offline with Orange and STC to move 16:00 GMT+1 next year. In principle keep weekly meetings during January/February and review later periodicity. + +### Next Steps +- Meetings schedule to be performed to begin at 16:00 Wednesdays next year (avoid collisions with Commonalities WG). @PedroDiez to generate issue and related PR. +- Next Meeting 18/JAN diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18.md new file mode 100644 index 0000000000000000000000000000000000000000..0c7a63181070a7673a900bb16adbaa2e524b00be --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-18.md @@ -0,0 +1,41 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 18-jan-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Gareth Williams (GSMA) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeenuddin Mohammed (STC) +- Tanwir Fahad (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Planning next steps in WG
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange | Update readme.md file to indicate that 2 flavors are defined + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Documentation and yaml of both proposals available. Version v0.5. Brief summary explanation of the status of the working group for new participants to have some context about work carried so far +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange proposes to align Carrier Billing API error structure with regards to commonalities error model defined. It is agreed to do so as it was a pending action from last year.
                                                        • This aligment will be done in v0.6.
                                                        • Telefonica comments will also apply and from its side some fetaures are still pending to be included (notifications, 1-step payment, list of payments).Maybe notifications model will be included along with error aligment
                                                        • v1.0 is targeted to have both proposals aligned with first set of functionalities.
                                                        • Pull Requests to be generated by Orange and Telefonica +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Traversal track coming from Commonalities WG. Intention is to have a Glossary Terms information within CAMARA with relevant terms of each WG.
                                                        Agreed to use the issue to compile relevant terms and definitions within WG (everyone can contribute) and once agreed Pedro will check with commonalities WG how to incorporate to the document (i.e trigger Pull Request) +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange proposes to add some explanation in README.md file of WG "root" folder about the existance of two flavours of APIs to facilitate the understanding of the situation within the WG.
                                                        Agreed to do so and move forward. Orange will elaborate proposal and generate Pull Request +ERICSSON questions | Ericsson asks some questions about both proposals. Mainly to know the difference between them (mainly the separation of concepts of purchase and payment in Telefonica porposal) and understand the working behaviour. Lifecycle of both proposals is also explained.
                                                        Regarding Telefonica proposal Ericsson asks about lifecycle of Purchases (how to manage Purchases that are never been tried to be payed). Telefonica will check how it manages it, although commented severals options may be implemented. Also about the use of fee, that will be internally checked. It also comments about possibility to provide order_id with another name. It is commented in the short/mid term it is not intended to be changed. +STC questions | STC comments will send offline some questions/doubts about Telefonica proposal + + +### Next Steps +- Next Meeting on 25th January diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25.md new file mode 100644 index 0000000000000000000000000000000000000000..222b52e5245195c5aa6ce5ec9b77c1ad1d7e9e90 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-01-25.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-jan-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues and Ongoing PRs
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) | Orange | Update readme.md file to indicate that 2 flavors are defined +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | Orange | Update README.md file - PR associated to [Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model + + +### Items Discussion + +Item | Discussion +---- | ---- +Management Topics | Ajit, Fahad and Nayeemuddin access to WG. Provided offline instructions after meeting to Ajit and Nayeemuddin to manage subscription to WG. Once subscription done and with Githug users, they should have access to WG documentation and discussion tracks. +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | PR associated to Issue 46.
                                                        Reviewed by Telefonica, given approval. Minor comment after the meeting provided. @ALL to provide any additional comment until Monday 30th January EOD. +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange proposes to align Carrier Billing API error structure with regards to commonalities error model defined. It is agreed to do so as it was a pending action from last year.
                                                        • This aligment will be done in v0.6.
                                                        • Telefonica comments will also apply and from its side some features are still pending to be included (notifications, 1-step payment, list of payments).Maybe notifications model will be included along with error aligment
                                                        • v1.0 is targeted to have both proposals aligned with first set of functionalities.
                                                        • Pull Requests to be generated by Orange and Telefonica +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange contribution to deal with Issue 44 and Issue 47. Telefonica provides some comments and see proposal coherent in general. Discussion over it:
                                                        • Agreed to do version update over same YAML (Telefonica to do the same on its contribution).
                                                        • "status" pattern "^[4-5][0-9]{2}$". Commented it is a point to reflect in Commonalities. Telefonica indicates it will comment internally to reflect it in commonalities so in every API this pattern can be indicated in YAML.
                                                        • Notification Model: Telefonica asks about behaviour of "notificationAuthToken" concept. Orange indicates it is a "Token" generated by client side and inserted as Authorization in notification from Payment server back to client. It is based in QoD model currently. Telefonica understands this and it comments this is not closed on its model so far (some solutions could be applied) and it is also not seen as the best approach to secure a notification. Ericsson also comments in that way. What is clear it is a common solution for any API is required, so probably it is a point for Commonalities WG. Orange shares view this is a topic for commonalities. Telefónica will check internally this. +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica contribution to deal with Issue 44 and Issue 47. Introduced from a high level poitn of view. Participants need to look into detail. Orange advises YAML seems to be some validation error. To be reviewed by Telefonica and update PR +Questions around APIs Proposals | • Q1-ERICSSON: Checkout - Management of Purchase LifeCycle: In Telefonica solution, an offline process runs to delete Purchases not attempted to be paid after some time. Other solutions could be marked them with an specific status. It depends also in Business Requirements.
                                                        • Q2-ERICSSON: Checkout - merchant.fee: Why this param is mandatory when a given contract indicating this is signed in advance. Already queried and waiting response on it.
                                                        • Q3-STC: Payment - Management of taxes: STC indicates it is needed in some way to indicate if an amount includes taxes or not. Orange comments "taxAmount" is an optional parameter in case merchant wants to indicate it. Ericsson porposes to have a boolean to indicate if "amount" has taxes. Orange requested Ericsson to open an issue to follow this.
                                                        • Q4-STC: Both Proposals: Return transaction time of a payment in response (a timestamp). Need to Open an issue on it to detail and provide a way forward. It can make sense to have it.
                                                        • Q5-STC: Checkout: Concept of merchant.id why is mandatory, because it may be identified by API client credentials (Orange for instance do in that way). Comment is in line of making it optional so only provided when merchant is different from API requester. Telefonica checks this in order to see if can be settled to optional adding an exception in case for any case it is required.
                                                        • Q6-STC: Checkout: Offline questions raised to telefónica proposal. To be compiled in an issue to have track of them. + + +### Next Steps +- Next Meeting on 01st February diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01.md new file mode 100644 index 0000000000000000000000000000000000000000..d93495ddf796061f93078c1d3f6ec5631fda0515 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-01.md @@ -0,0 +1,51 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 01-feb-2023
                                                        +**Status:** FINAL + +## Attendees +- Gareth Williams (GSMA) +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Generate a Tag for v0.5
                                                        +Review of Issues and Ongoing PRs
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47] (https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment + + +### Items Discussion + +Item | Discussion +---- | ---- +Management Topics | Management of Users. Still not seeing in GitHub some collaborators. @Pedro contact Markus offline. DONE after the meeting +Generate Release Tag | Commented during meeting. Generate a Realease Tag to compile work done so far. No official version yet. Also versioning approach being discussed in Commonalities WG. DONE after meeting: https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.5.0 +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Comments provided by Orange about Glossary Definitions. Suggestions seen OK by Telefonica. New proposal about "Purchase" concept given by Telefonica. @ALL review thread. DEADLINE for this thread is EOW of Week 06. After that glossary proposal will be trigger into Commonalities WG +[Pull Request 49](https://github.com/camaraproject/CarrierBillingCheckOut/pull/49) | MERGED. Associated [Issue 46](https://github.com/camaraproject/CarrierBillingCheckOut/issues/46) CLOSED +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange contribution to deal with Issue 44 and Issue 47. Given OK by Telefonica. Waiting any more comment during this week +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica contribution to deal with Issue 44 and Issue 47. Telefonica comments it is going to update based on output of some parameters that probably can be set as optional, so indicates to await until that is done to be reviewed. It will inform of that +Questions around APIs Proposals | Issues already created: Issues 54, 55, 56, managed as a set of tasklist +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica provided feedback to questions 2 and 4. Questions 5,6,7 currently being checked, probably there is room to set some params as optional. Questions 1 and 3 are pending from internal analysis. Regarding Question 1, Use Case is for instance a vending machine SW that needs to input user's msisdn to perform payment (based in a client credentials model, without involving user authentication) +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Orange comments it is ok about the issue and will provide a proposal in a next version. Commented during the meeting is is not urgent. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | After some discussion, it is discarded to indicate timestamps in requests to avoid inconsistencies and implementation complexity. At response level, it makes sense to have two "timestamps", date when the payment is created and date when the payment is effectively performed (optional). Summary provided by Orange in the issue with initial params proposal. +AoB | • **Notifications**: It is share common view that notifications management is a traversal topic. In this meeting besides notification securization is also mentioned how notification_url is provided. Currently, a dynamical approach is followed, also TMForum is referenced as other option (Registration of notification_url). About securization Telefonica indicates that, before triggering any discussion in CAMARA internal analysis has to be done from its side.
                                                        • **APIs Family**: Ericsson comments about the topic of having only one approach (API favor) in this WG. Orange indicates that this should be the final picture in the WG, only having one option. Telefonica indicates it does not see opening this topic at least during this year, because currently is focused in providing new functionality to de BC Checkout proposal based on Business Requirements, although it understands it is the theorectical purpose of CAMARA of having a unique option for each track. Orange does not share the same view and thinks it is a topic to be analyzed in the short-term. + + +### Next Steps +- Next Meeting to be managed. Collision with Commonalities WG meeting, looking for a date after meeting diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15.md new file mode 100644 index 0000000000000000000000000000000000000000..7e28307d54dbef71a1a921cdbb3fd8c551f8a416 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-15.md @@ -0,0 +1,51 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 15-feb-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Nayeemuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | Orange | Improve payment API (v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and [Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | Telefonica | Improve_Checkout_Model_Error_and_Notifications_(v0.6) - PR associated to [Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) and support for Notifications Model +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String + + +### Items Discussion + +Item | Discussion +---- | ---- +Working Group Management | Rafał, Fahad and Nayeeem have already access into WG. Can be requested as reviewers. New member from STC presented in the meeting: Naeem Ur Rehman +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Proposed to be closed. Notifications model has relevance to be a traversal track in commonalities. Pending feedback from Orange that cannot attend meeting +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | If no further comments today/tomorrow, terms indicated with its meaning will be the ones proposed by Pull Request in Commonalities. Commented into WG for any final refinement or additional term. +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Proposed to be closed. Notifications model has relevance to be a traversal track in commonalities. Pending feedback from Orange that cannot attend meeting +[Pull Request 50](https://github.com/camaraproject/CarrierBillingCheckOut/pull/50) | MERGED. CLOSED +[Pull Request 51](https://github.com/camaraproject/CarrierBillingCheckOut/pull/51) | MERGED. CLOSED +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica still analyzing questions Q1 and Q3. Intention is to address them along with new API Proposal by TEF (covering 1-STEP and list of purchases). Probably MSISDN included, however under internal analysis. +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Indication in Payment approach whether amount has taxes. Targetted for a higher version. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Regarding payment relevant dates, proposal done by Orange.
                                                        • Telefonica: indicates that makes sense the proposal and will include that info as optional. It is pending to discuss about inclusion in notifications body. Need also Orange's view on it.
                                                        • Telefonica: taken advantage of this thread it is commented the need of align input/output parameters in snake_case format. That is something to guarantee by API proposals for v1.0. +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Keep this topic open until a common view of Error Model is aligned in CAMARA. API Proposals will have to be aligned in that way +AoB | • **Notifications**: Commented it is traversal topic. Telefonica internally working before open issue un commonalities (in a couple of weeks at least).
                                                        • **APIs Family**: STC comments about the the topic of having only one approach (API favor) in this WG. Orange and Ericsson already commented last week they expect one API favor. Telefonica comments it is not seen in the short-term unless coming a guideline from "upper layers". Currently, both APIs have different concepts approach on how to address E2E behaviour. Also both APIs need to be aligned in terms of functionalities in order to check synergies in advance. + + +### Next Steps +- Next Meetings: Week of 27th February is MWC week
                                                        + • 22th February (same datetime)
                                                        + • 8th March (same datetime)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22.md new file mode 100644 index 0000000000000000000000000000000000000000..90da9b27bfcd5f6464f8b336b4fe4528a111550c --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-02-22.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-feb-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan R (ERICSSON) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Orange | Align Error Structure with design guideline +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Commonalities (Shilpa) | Update commonalities glossary with subproject relevant terms +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Orange | Add notification authorization token in POST Request +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml + + +### Items Discussion + +Item | Discussion +---- | ---- +Working Group Management | +[Issue 44](https://github.com/camaraproject/CarrierBillingCheckOut/issues/44) | Set to CLOSED. +[Issue 45](https://github.com/camaraproject/CarrierBillingCheckOut/issues/45) | Set to CLOSED. Contributed to [Commonalities Pull Request 120](https://github.com/camaraproject/WorkingGroups/pull/120) +[Issue 47](https://github.com/camaraproject/CarrierBillingCheckOut/issues/47) | Set to CLOSED. +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica proposal to be presented yet, not possible to present this week due to internal matters. That is reason to keep Q1 and Q3 open. Indication of phone_number is foreseen as needed in some scenarios (WiFi, Fixed-Access, where mobile line can not explicitly identified by authentication process). When presenting proposal, rationale will be provided along with it. Ericsson also comments in this way, about the need of msisdn. Pending proposal by Telefonica, expectation is to have it during next week, so presented for the next meeting. +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Indication in Payment approach whether amount has taxes. Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Regarding payment relevant dates, proposal done by Orange. Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Keep this topic open until a common view of Error Model is aligned in CAMARA. API Proposals will have to be aligned in that way. Referenced in [Commonalities Issue 151](https://github.com/camaraproject/WorkingGroups/issues/151) +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Generated issue by Orange (separated from Issue 56, where initially mentioned). Commented by Telefonica that mention of align proposals is to be compliant with Commonalities in the way moving forward towards v1.0. Orange indicates they would like to open an Issue in Commonalities to discuss this topic, as there are other approaches in the ecosystem (OMA, TMF,...). Issue opened after meeting [Commonalities Issue 157](https://github.com/camaraproject/WorkingGroups/issues/157). +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56). Explained both dates (paymentCreationDate and paymentDate) are included as optional in GET /payments and /payments/{id}. Also paymentDate is included in notification, to indicate when payment is effective.
                                                        • Ericsson is OK with the proposal as request coming from its side.
                                                        • Telefonica is also OK with the proposal, and share view about including paymentDate in notification as it makes sense to have a coherente working proposal. + + + +### Next Steps +- Next Meetings:
                                                        + • 8th March (same datetime)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08.md new file mode 100644 index 0000000000000000000000000000000000000000..4f3d11a5cd415b7a5c688b0d4fcbeed06f699c72 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-08.md @@ -0,0 +1,48 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 08-mar-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ziad H. (FOO.MOBI) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | WG | OPEN QUESTIONS - Carrier Billing Payment Proposal +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | WG | OPEN QUESTION - Adding Transaction time for a Payment +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Orange | Design Guidelines: HTTP Status Code type should be Integer, not String +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Telefonica provides answers for pending questions Q1 and Q3. Issue will continue open until WG review and give approval for [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) +[Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) | Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60). Set to CLOSED. +[Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56) | Managed in Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) and Carrier Billing Checkout by [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64). Set to CLOSED. +[Issue 58](https://github.com/camaraproject/CarrierBillingCheckOut/issues/58) | Commonalities Error Model is aligned in both proposals Carrier Billing Payment by [Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) and Carrier Billing Checkout by [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64). Set to CLOSED. +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Keep Opened. Being Evaludated in [Commonalities Issue 157](https://github.com/camaraproject/WorkingGroups/issues/157). Once taken a decision, actions will have to be performed within the proposals accordingly. +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56).
                                                        • Minor update change clarified and performed by Orange (remove pattern for HTTP status) during the meeting.
                                                        • Telefonica will review and give OK after the meeting. Ready to be merged +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | PR generated by Telefonica to provide functionality for 1-step payment and list of purchases. Besides this, it is taken advantage to also include:
                                                        • `payment creation date` and `payment date` concepts in Details of a purchase and List of purchases endpoints.
                                                        • In the same fashion, `payment date` concept is also included in notifications endpoint.
                                                        • Additionally, `phone number` concept is included in payment body request (for both 1-step and 2-step procedures), as optional input, due to the fact in some authentication scenarios (e.g. Mobile Connect Based, Mobile IP based) phone number can be obtained and therefore that information can be carried within Authorization header. This does NOT mean an implementation can consider this parameter as required always but to explain the rationale of the proposal
                                                        • Finally, HTTP `status` pattern is removed to be aligned.

                                                        Mentioned to be reviewed by the WG team after the meeting to provide comments and further doubts.
                                                        • Orange comments about two topics: The prevalence of the `phone number` request body param over Authorization information and in that way the scenario of having non-matching information between the value carried within this param and the information contained within Authorization header.
                                                        • Telefonica indicates the information present in this param is the one to be considered when provided (so it prevails over Authorization header info) to identify the `phone number` to be charged and it is a very good point the one raised about non-matching information between this param and Authorization Header, so it will be reviewed internally. +AoB | Telefonica comments that given both proposals are moving forward to have an aligment at functionality level and pending points are mainly related to Commonalities topics (input/output params format, notificatons approach) it makes sense to move to a bi-weekly meetings model, work offline about proposals and Commonalities alignment and having specific weekly meeting if situation requires for it (relevant topic). Orange shares this view, given that proposals are reaching a common level of maturity and pending points to have a first set of functionality are related to Commonalities topics. WG considers suitable this WoW model and no objection raised. Meetings will be scheduled for the next two months. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting planned for 22th March (same datetime)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29.md new file mode 100644 index 0000000000000000000000000000000000000000..2a2094dd6de5b4c60148b01c1d211582fefe9bf2 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-03-29.md @@ -0,0 +1,45 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 29-mar-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ludovic Robert (ORANGE) +- Naeem Ur Rehman (STC) +- Nayeenuddin Mohammed (STC) +- Pedro Díez (TELEFONICA) +- Sönke Peters (VODAFONE) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | Orange | snake_case guideline alignement +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | Orange | Update carrier_billing_payment.yaml +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Orange | Update Carrier_Billing_Payment_API.md + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Questions addressed and accordingly included in [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) +[Issue 61](https://github.com/camaraproject/CarrierBillingCheckOut/issues/61) | snake_case input/output params in APIs. Commonalities Guidelines Updated and changes being considered within this WG PR60 and PR64. Set to CLOSED. +[Pull Request 60](https://github.com/camaraproject/CarrierBillingCheckOut/pull/60) | PR generated by Orange to deal with [Issue 55](https://github.com/camaraproject/CarrierBillingCheckOut/issues/55) and [Issue 56](https://github.com/camaraproject/CarrierBillingCheckOut/issues/56).
                                                        MERGED. +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Updates regarding initial proposal: aligment with camelCase, includes pagination and exception when input phone number in payment does not match Auth context.
                                                        To be reviewed by the WG up to 12/Apr.
                                                        After its merging the same WoW will be done, updating related documentation. +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Update Documentation for Carrier Billing Payment v0.7.0.
                                                        Reviewed by Telefonica (given OK). Additional comments to be received up to Monday 03/Apr. If no further comments, it can be merged Monday 03/Apr EoD. +AoB | • WG next actions: Move forward towards an initial v1.0 version for both proposals. Main pending topics are probably related to notifications topics (being managed in Commonalities).
                                                        • Convivence of proposals: STC raised the topic, if there is a guidance from Steerco (rationale for them is to determine which proposal to implement). Telefonica indicates no news about it and from its point of view currently two proposals are in force. Oranges shares the view on deciding about one proposal and not only regarding this WG but also another WGs (Number Verification,...). Telefonica will check internally + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Pedro to align with Jose Antonio Ordoñez Lucena to avoid overlapping with IdentityAndConsentManagement WG meetings. DONE offline after meeting
                                                        + • Next meeting proposed to be on 13th/April - 12:00 CEST
                                                        + • Rest of scheduled meeting series do not overlap with IdentityAndConsentManagement WG
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13.md new file mode 100644 index 0000000000000000000000000000000000000000..8a36e09e781b9ddcdc6b085d83ed478168f22db6 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-13.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 13-abr-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ludovic Robert (ORANGE) +- Fahad Tanwir (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | WG | OPEN QUESTIONS - Carrier Billing Checkout Proposal +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Telefonica | carrier_billing_checkout_1-step_model_and_purchases_list +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Orange | Update Carrier_Billing_Payment_API.md + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 54](https://github.com/camaraproject/CarrierBillingCheckOut/issues/54) | Questions addressed and accordingly included in [Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64).
                                                        Set to CLOSED as covered in Pull Request 64. +[Pull Request 64](https://github.com/camaraproject/CarrierBillingCheckOut/pull/64) | Update carrier_billing_checkout_1-step_model_and_purchases_list (v0.7.0 aligned in features with Payment proposal). MERGED
                                                        After its merging the same WoW will be done, updating related documentation. +[Pull Request 66](https://github.com/camaraproject/CarrierBillingCheckOut/pull/66) | Update Documentation for Carrier Billing Payment v0.7.0. MERGED + + +### AoB + +WG next actions:
                                                        + +• Notifications Guideline Track (initial baseline) is being completed within [Commonalities PR#173](https://github.com/camaraproject/WorkingGroups/pull/173). Once completed, main pending point is to address impact/discussion in current notifications approach. Probably better way is an issue to open discussion over it, before proposing any change if any. That is main point to move proposals towards a v1.0 (apart from documentation topics).
                                                        + +• Documentation track: Pending to incorporate into OpenAPI proposals full autocontained documentation model as per [Commonalities Issue#164](https://github.com/camaraproject/WorkingGroups/issues/164). Orange highlights made a question about images, and it seems it can be possible (in Carrier Billing there are sequence diagrams). Both Orange and Telefonica will make tests to check all information can be accommodated within OpenAPI yaml.
                                                        + +• Convivence of proposals: Telefonica has commented internally, in order for Business to be aware of situation and for them to be able to do product checkings and also has contacted to have business contacts from some Telco Operators.
                                                        + +• STC indicates they have some concerns about the proposals and will make some contribution regarding it. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting - 26th April - 16:00 CEST diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26.md new file mode 100644 index 0000000000000000000000000000000000000000..0c4bf68039e381059f705ad3f77075f6bd308e20 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-04-26.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 26-abr-2023
                                                        +**Status:** FINAL + +## Attendees +- Rafał Artych (DT) +- Ajit Raghavan (ERICSSON) +- Ludovic Robert (ORANGE) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) +- Claudio Di Padova (VODAFONE) +- Mariusz Dawidowicz (VODAFONE) + + +## Goals +Review of Issues/PRs and next steps
                                                        + +Item | Who | Description +---- | ---- | ---- +Welcome to newcomers | WG | New attendants within WG:
                                                        • Jorge García Hospital (TELEFONICA): Product Owner of Telefonica in GSMA OpenGateway initiative.
                                                        • Claudio Di Padova (VODAFONE): VF Germany Product owner for Payment products (among other features).
                                                        • Mariusz Dawidowicz (VODAFONE): Product Manager in VF regarding Charging Services +[Issue 69](https://github.com/camaraproject/CarrierBillingCheckOut/issues/69) | WG | Manage Documentation +[Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70) | Telefonica | Fake PR to test model for inclusion of images + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 69](https://github.com/camaraproject/CarrierBillingCheckOut/issues/69) | Test successfully performed within [Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70), we can move forward. In order to move forward Pedro will comment within [Commonalities Issue 164](https://github.com/camaraproject/WorkingGroups/issues/164) and will wait for Commonalities output before to update the documentation +[Pull Request 70](https://github.com/camaraproject/CarrierBillingCheckOut/pull/70) | Fake PR to test model for inclusion of images within "description" field of API dcoumentation. CLOSED after meeting +AoB | **Subscription (within Notifications Commonalities Track):**
                                                        • Discussion on Subscription path still open - Ludovic will modify the PR and send back to review to Artych, Pedro & Eric.

                                                        **Other topics:**
                                                        • Pedro explained existing flavors managed in the project.
                                                        • Pedro and Telefonica is working on an aggregated proposal and will reach Orange for finding a consensus.
                                                        • Question on business/product side: this is driven in a GSMA Open Gateway Business stream (not a CAMARA project). + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting 10-may-2023
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24.md new file mode 100644 index 0000000000000000000000000000000000000000..1a1de831c8823b5a3dab65e9683d3ec510b98af7 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-05-24.md @@ -0,0 +1,34 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 24-may-2023
                                                        +**Status:** FINAL + +## Attendees +- Fahad Tanwir (STC) +- Naeem Ur Rehman (STC) +- Jorge García Hospital (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG | Decision in CAMARA API for Carrier Billing +[Several Issues] | Huawei | Several Issues Opened by Huawei (Miranda Tsing) more details below + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Issue opened based on topics/discussion already kept within WG.
                                                        • Orange (Ludovic) could not attend meeting but advised in advance about the opening of the issue. Agreed to upload [PR#78](https://github.com/camaraproject/CarrierBillingCheckOut/pull/78) as supporting documentation.
                                                        • STC looks good to open the issue and be able to manage this topic as it is needed an aligned solution.
                                                        • Commented during meeting, with the aim of reaching a conlusion and have a way forward within this WG.
                                                        • Being internally checked also with Markus under which conditions a votation can be performed within WG or needs to be addressed via TSC.
                                                        • After meeting (26/May), Orange indicates their preference of managing this topic at TSC level. +[Several Issues] | Several Issues opened by Huawei. Company is interested in contributing in this WG. Issues to be addressed offline during next two weeks (Issues 73, 74, 76, 77). Miranda joined meeting once finished. Pedro talk to her offline in order to comment about next meeting so she can join, introduce herself into the WG and participate in meetings. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting 7th June (To Be Scheduled). 16:00 - 17:00 CEST
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28.md new file mode 100644 index 0000000000000000000000000000000000000000..80fa7bc6c224f60f8aab4b686553fe122b65802b --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-06-28.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-jun-2023
                                                        +**Status:** FINAL + +## Attendees +- Toyeeb Rehman (GSMA) +- Ajit Raghavan (ERICSSON) +- Elisabeth Mueller (ERICSSON) +- Shuting Qing (HUAWEI) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Ad-hoc meeting to present joint Orange-Telefonica proposal
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | WG | Decision in CAMARA API for Carrier Billing +[Issue 87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Orange-Telefonica | Joint Carrier Billing Proposal +[Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica | ORA_TEF_CarrierBilling_joint_proposal-Issue87 + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue 79](https://github.com/camaraproject/CarrierBillingCheckOut/issues/79) | Issue CLOSED. Agreement reached between Orange and Telefonica. New Proposal presented +[Issue 87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Rationale for the agreement and joint proposal presented by Orange and Telefonica. Compiles the basis and key pòints for the new proposal. Kept open until [Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) is merged. +[Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica joint proposal. Proposal explained. Main output points:
                                                        • Good reception by WG members which consider a good starting point to move forward within WG.
                                                        • Some adjustments to be performed after proposal presentation (To be documented in PR description for transparency), regarding error scenarios. **AP@Pedro Díez** to manage opening of topics/issues in Commonalities (Link HTTP 400 to OUT_OF_RANGE, Fixed INVALID_ARGUMENT typo).
                                                        • Ericsson asks for rationale of making phoneNumber opctional. There can be scenarios where phoneNumber can be identified via Access Token (i.e Authorization header info). Anyway it is an open topic in GSMA OGW how to align access to APIs.
                                                        • Ericsson asks for enabling the filtering of payments associated to a given merchant. Orange indicates in initial proposal "fields" value was supported. Telefonica comments that in this case what it is needed is to only return payments related to a given condition not related to only return some fields of the response. Seen as valuable point to address. **AP@Ludovic** to open issue in Commonalities.
                                                        • PR open for comments in the next week. Aim is to merge this initial proposal on 12th July week. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting TBD. **AP@Pedro Díez** to propose dates for summer period
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19.md new file mode 100644 index 0000000000000000000000000000000000000000..5a98a721a601707d6fedd3b20501ed4ac5021745 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-07-19.md @@ -0,0 +1,53 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 19-jul-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ajit Raghavan (ERICSSON) +- Masaharu Hattory (KDDI) +- Ludovic Robert (ORANGE) +- Philip Lengyel (TELEFONICA GERMANY) +- Agustín Martín (TELEFONICA) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Orange-Telefonica | Joint Carrier Billing Proposal +[PR#88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica | ORA_TEF_CarrierBilling_joint_proposal-Issue87 +[PR#81](https://github.com/camaraproject/CarrierBillingCheckOut/pull/81) | Huawei | revise meeting info +[Issue#73](https://github.com/camaraproject/CarrierBillingCheckOut/issues/73) | Huawei | Update Github PR Template +[PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72) | Huawei | Github PR Template +[Issue#76](https://github.com/camaraproject/CarrierBillingCheckOut/issues/76) | Huawei | Business Scenario for Carrier Billing Check Out +[PR#75](https://github.com/camaraproject/CarrierBillingCheckOut/pull/75) | Huawei | Add a business scenario slide +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Telefonica | Summer Meetings Planning +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Ericsson | Improvement suggestions for merged API + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#87](https://github.com/camaraproject/CarrierBillingCheckOut/issues/87) | Rationale for the agreement and joint proposal presented by Orange and Telefonica. Issue CLOSED. [Pull Request 88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) is merged. +[PR#88](https://github.com/camaraproject/CarrierBillingCheckOut/pull/88) | Orange-Telefonica joint proposal. MERGED to have initial proposal to move forward +[PR#81](https://github.com/camaraproject/CarrierBillingCheckOut/pull/81) | revise meeting info. Updated meeting Info. MERGED +[Issue#76](https://github.com/camaraproject/CarrierBillingCheckOut/issues/76), [PR#75](https://github.com/camaraproject/CarrierBillingCheckOut/pull/75) | Business information provided by Huawei. Commented it fits better within GSMA OGW initiative. CLOSED +Generic Note | Commented in meeting that summary of Issues/PRs being carried in the last month will be reflected to have track of progress, even not mentioned / discussed in meeting. See topics above. Also, it is indicated a new issue will be opened (Telefonica) to compile documentation that has to be deleted/updated according to existance of a common proposal. +[Issue#73](https://github.com/camaraproject/CarrierBillingCheckOut/issues/73) | Update Github PR Template. Issue to inform about adapting GitHub templates defined in Commonalities to Carrier Billing Working Group. Being carried in [PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72). CLOSED after meeting +[PR#72](https://github.com/camaraproject/CarrierBillingCheckOut/pull/72) | Github PR Template. Some adjustments commented by Rafal (bug template and labels) and performed respectively by Shuting and Pedro. After meeting, "bug template" is removed and PR is MERGED.## +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Commented planned dates for the next meetings. Bi-weekly period to be recovered in Autumn. Ericsson and Orange indicates dates are fine for them. No objections. Next meetings will be scheduled accordingly. Huawei provided comments within this issue, however does not attend the meeting. If any comment, it will be driven within the issue. +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Issue opened By Ericsson with the aim of defining valuable filter criteria for the GET /payments endpoint. Some initial comments by Ericsson, Orange and Telefonica compiled in issue. Discussion about filtering:
                                                        • First, we need to provide mechanism to 'waterproofing' between API client. Technical credential could be used for that but it must be documented. Ludovic (Orange) will raise the point to commonalities as this 'data sealing' must be done for any API providing a capability to retrieve a list. Pedro (Telefonica) comments that this logic makes sense within carrier billing, due to it may compromise privacy and legal implications that a given API client can kave access to payments triggered via a different one and not sure about the traversal applicability of this in other tracks, anyway open an issue in commonalities is fine to have traversal view about this.
                                                        • Second, for specific carrier billing filtering criteria, Pedro will create a PR to get consensus within working group for a set of criteria. Ajit (Ericsson) provided some suggestion within the meeting. +AoB | Ajit (Ericsson) raised a point about tax: if `isTaxIncluded` is false how the tax is computed? In this case the BE system will require the service (and product) id to calculate tax accordingly. This is an implementation issue to be sure service id (and product id) are related to tax code.

                                                        Management of recurring payments and refunds - Need to be discussed in the product stream (not prioritized right now). Pedro (Telefonica) will create 2 issues to collect feedback for Refund and for Recurring Payment respectively. + + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meetings: 23th-AGO, 06th-SEP
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23.md new file mode 100644 index 0000000000000000000000000000000000000000..762d3e33c8beabab4a8ab6da149d77014945cc18 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-08-23.md @@ -0,0 +1,39 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 23-aug-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Telefonica | Summer Meetings Planning +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Ericsson | Improvement suggestions for merged API +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Telefonica | Documentation Update in Carrier Billing WG +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#90](https://github.com/camaraproject/CarrierBillingCheckOut/issues/90) | Dates already managed. Next meeting September, 6th will be moved one hour later than planned (17:00 CEST) to avoid collision with Identity/consent WG meeting. In that meeting, it will be talked about resume bi-weekly meetings. CLOSED +[Issue#91](https://github.com/camaraproject/CarrierBillingCheckOut/issues/91) | Related [PR#96](https://github.com/camaraproject/CarrierBillingCheckOut/pull/96) generated few weeks ago.
                                                        Main topic addressed is adding filtering attributes (using commonalities design guideline 'grammar') in `GET /payments` operation, and also align description for date-time fields format. `paymentCreationDate` is set to mandatory in response model. During the meeting it is commented that some adjustment is needed with regards to the date filtering to be more explicit. Pedro will do after meeting. If no further comments PR will me merged in one week from now.

                                                        We propose to keep the version in 0.2-wip as changes are coming on notification in particular for notification format (specific or cloud event) and for the introduction of using callback (like in qod). +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Documentation Update in Carrier Billing WG. Issue opened to manage WG repo updates with current "picture" status. Already covered 3 of 4 tasks. Related actions/PRs:
                                                        • WG renaming discarded after checking with Markus (huge effort). DONE/CLOSED.
                                                        • [PR#94](https://github.com/camaraproject/CarrierBillingCheckOut/pull/94). Move old proposals to `/documentation/supportingDocuments` folder. DONE/CLOSED.
                                                        • [PR#95](https://github.com/camaraproject/CarrierBillingCheckOut/pull/95). Update `README.md` at 'root' directory. DONE/CLOSED.
                                                        • Update documentation in `/documentation/API_documentation/` folder. Pedro and Ludovic will check offline to identity documentation to be updated and generate subsequent PRs required. OPEN. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Two topics raised:
                                                        • Enhancement of the look & feel. Pedro (TEF) makes a proposal for a better look & fell for the errors. Ludovic (ORA) indicates is probably good to see how is it described in other API and in particular in QoD and perhaps propose a same look & feel across all APIs. Pedro will also check APIs in other WGs. Rafał provides also reference to Commonalities Issue [#31](https://github.com/camaraproject/Commonalities/issues/31) within this context.

                                                        • Notifications design. Related to Commonalities Issues [#8](https://github.com/camaraproject/Commonalities/issues/8) and [#44](https://github.com/camaraproject/Commonalities/issues/44). Based on agreement reached, probably would be needed to re-design notification endpoint. That is also reason to keep current version as v0.2.0-wip. Ludovic (Orange) comments is reasonable this way forward. +AoB | • Mohammed (STC) asks about Token lifetime conventions. Both Ludovic (ORA) and Pedro (TEF) comments that this topic is a matter of implementation and up to security considerations in each Operator.
                                                        • Mohammed (STC) also asks about recurring payments functionality. Pedro (TEF) indicates currently the WoW is for new features to be agreed in GSMA Open Gateway before going to CAMARA. In case of TEF and ORA there is also interest and TEF is considering/pushing this in GSMA. Pedro will provide Mohammed contact with TEF/ORA product members. + +### Next Steps +- Next Meetings:
                                                        + • Agreed to move forward by Bi-weekly meetings. Exceptional weekly meeting could be arranged on demand if any topic of relevance is raised
                                                        + • Next meeting: 06th-SEP, 17:00 - 18:00 (CEST)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06.md new file mode 100644 index 0000000000000000000000000000000000000000..cdec6c7dea0a676d520121fcaec5cf78fc3d9d7d --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-06.md @@ -0,0 +1,37 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-sep-2023
                                                        +**Status:** FINAL + +## Attendees + +- Masaharu Hattori (KDDI) on behalf of Toshi +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Update Working Group Status +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Telefonica | Documentation Update in Carrier Billing WG +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#101](https://github.com/camaraproject/CarrierBillingCheckOut/issues/101) | Orange | Fix `x-correlator` type (should be `X-Correlator`) + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | So far, **initial v0.2.0-wip is merged** including mainly filtering rules to common proposal. Next steps are dependant on output from commonalities (Notifications, securitySchemas, datetime format,...). It is expected to begin to work in a consistent v0.2.0 at the end of september so as it probably can be tagged as the first release of Carrier Billing (will talk at that time). +[Issue#93](https://github.com/camaraproject/CarrierBillingCheckOut/issues/93) | Documentation Update in Carrier Billing WG. Work offline between Orange (Ludovic) and Telefonica (Pedro) to manage pending actions and distribute work. 2 PR have been triggered:
                                                        • [PR#99](https://github.com/camaraproject/CarrierBillingCheckOut/pull/99) to remove documentation no longer required - some documentation will be removed once we complete the yaml documentation of the API spec.
                                                        • [PR#100](https://github.com/camaraproject/CarrierBillingCheckOut/pull/100) to remove checkout word + update Model.
                                                        Both PRs were cross-reviewed by Ludovic and Pedro respectively and gave OK. They have been MERGED after the meeting. Issue is CLOSED. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Two topics raised:
                                                        • **Enhancement of the look & feel**. Pedro indicates not able to address look&feel situation in other APIs. So Look & feel across API will be done later and resume this topic of the issue.

                                                        • **Notifications design**. Waiting to commonalities outcomes. Related to Commonalities Issues [#8](https://github.com/camaraproject/Commonalities/issues/8) and [#44](https://github.com/camaraproject/Commonalities/issues/44). Pending on the output of those issues, related PRs are [Commonalities-PR#43](https://github.com/camaraproject/Commonalities/pull/43) and [Commonalities-PR#56](https://github.com/camaraproject/Commonalities/pull/56) respectively. +[Issue#101](https://github.com/camaraproject/CarrierBillingCheckOut/issues/101) | Understood the rationale of the issue. Pedro (Telefonica) comments HTTP headers are case insensitive so both Uppercase and lowercase are valid. Ludovic (Orange) closed the issue after the meeting. Issue is CLOSED +AoB | • STC (Mohamed E. Ali) wishes to get business discussion on new features (refund, recurrent payments) - Pedro (pedro.diezgarcia@telefonica.com) will make Mohamed in contact with TEF (Agustin) & Orange business (Patrick Berthie).
                                                        • Next meeting Sep, 28th (at 4.00 CEST) and then get back on nominal schedule from Oct, 11th + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 28th-SEP, 16:00 - 17:00 (CEST)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28.md new file mode 100644 index 0000000000000000000000000000000000000000..6d222ae429adb86f4d52fc3a1480d9dbd99db4a0 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-09-28.md @@ -0,0 +1,33 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 28-sep-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Update Working Group Status +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Next steps are to work in a consistent v0.2.0, addressing several issues:
                                                        • Commonalities related: securitySchemas, notifications guidelines.
                                                        • Enhancing API documentation in API spec.
                                                        • Fixing some topics (e.g. adding 404 Exception to endpoints that have paymentId defined in path) and gaps.
                                                        Several issues will be opened and reuse a common PR to work on. Some comments from Ludovic (Orange) about securitySchemes for query endpoints (GET) to be used in 2-legged mode, to be discussed further. With all of this, an initial release would be tagged. Rafał (DT) also comments in this way in order to have an initial release. +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Regarding the topic of **Enhancement of the look & feel** Pedro (TEF) will take a look to other WGs next week. Regarding **Notifications design** it will be addressed with commonalities output. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 11th-OCT, 16:00 - 17:00 (CEST)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11.md new file mode 100644 index 0000000000000000000000000000000000000000..dc1e7091c0f755d94ea7a3fc22a2ebd44c7043c4 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-11.md @@ -0,0 +1,49 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 11-oct-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | External | Refund functionality for Payment requests +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Deutsche Telekom | Type representing money values +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Telefonica | Enhancement of Documentation within API OAS yaml +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Telefonica | # Add 404 Exception to other API endpoints that have {paymentId} in API path +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Telefonica | API Spec aligment with Commonalities securitySchemes, security and scopes +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Orange | Align Carrier Billing Event with CloudEvents structure + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Limited scope to topic of **Enhancement of the look & feel** (Notifications aligment covered in [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112). Action Point to Pedro to provide info to the WG. Deadline is 16th October +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | Issue opened externally. Good to be tracked. Fair request from a technical perspective.
                                                        • TEF (Pedro) comments in advance TEF Product side will probably ask for this functionality during this year.
                                                        • ORA (Ludovic) will also check for Product view internally.
                                                        Commented during the meeting the product side could be trickier (depending on country regulations for example). Need to be addressed after tackling current issues in progress. Comments from the team are welcome. Need to synch with GSMA OGW product stream which manage API requirement drop.
                                                        • STC (Mohamed) raised a question about managing technical issue where we have several payments for same interaction. Scenario can be managed with the use of the `clientCorrelator` field so as we should not have this problem.
                                                        • STC (Mohamed) also explained the requirement for reversal vs refund. There are distinctions between reversal (time-limited, in case of STC is End Of Business Day, this is to reverse a payment, the merchant will not get charged for this) and refund (this is a new transaction independent from a payment, merchant is charged for that). This is a good point for Refund thread. Action Point for Mohamed to comment in the issue. +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | DT (Rafał) introduces the topic. It aims for modeling amounts in a way it may be used worldwide, allowing to tackle the disparity of decimal (0,2,3) in different countries around the world. Proposal here is to use long integer for amount and depending on the currency we deduct the decimal. WG agrees to gather more feedback on this issue and continue discussion. +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Issue to deal with Commonalities guideline of having full API documentation within API Spec. TEF (Pedro) will use our initial Markdown documentation & incorporate it (and refresh) in the yaml, generating a new PR. Further updates would be required based on output of other issues discussion (e.g. [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110)). Agreed by the team. +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Issue opened to reflect the fact that other endpoints (`preparePayment`, `confirmPayment`) has the same scenario of a non-existing Payment Identifier as `retrievePayment`, so 404 NOT_FOUND exception is needed. Agreed by the team, to be handled in same PR than [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106). +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Dealing with two Commonalities topics alignment:
                                                        • **securitySchema**: need to wait Commonalities (or TSC) outcomes - Commonalities PR: [Commonalities#57](https://github.com/camaraproject/Commonalities/pull/57).
                                                        • **scopes**: we can go with the way proposed in the issue and proceed within the same PR. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Issue driven by implementation feedback. Case risen due to the fact no filter criteria is mandatory to be provided, to have an alignment about given response. Use of page/perPage is defined Commonalities. The proposal here is to provide default value, so we can also improve performance in the response time.
                                                        • ORA (Ludovic) indicates we need probably another error code when the request is too vague/wide (too many records match the filtering criteria), for instance, payments whose "transactionOperationStatus" is equal to "succeeded". Given also the fact the initial baseline was to return all registries when no filter criteria was indicated. Additional thinking is required regarding this issue. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Trigger is the identification of "denied" scenarios in 2-STEP Payment (i.e. user is blocked when trying to confirm payment). Based on that, also other points are covered for alignment of lifecycle understanding. Further discussion / thinking is required on this. Some points compiled so far:
                                                        • Exception 403 Payment Denied for two-step confirmPayment
                                                        • Discussion on sync one-step payment: probably the only state is succeeded when the payment resource is created while for async we can have Denied (from Processing state). This is not reflected on the current state engine.
                                                        • A new event is required for Payment denied. Team agreed.
                                                        • Discussion about when the balance is checked for the two-step payment: When the payment is `reserved` the money is blocked. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Not covered during the meeting. To be handled in next meeting. Kindly ask offine review. +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | ORA (Ludovic) remarks the need of Notifications alignment with commonalities. It is needed to be covered. Agreed by the team. To be considered within PR. Pedro and Ludovic will talk offline to manage PR(s) in the best way. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 25th-OCT, 16:00 - 17:00 (CEST)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25.md new file mode 100644 index 0000000000000000000000000000000000000000..0bf39f8fb310a7892763af954df7e044c55e472b --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-10-25.md @@ -0,0 +1,58 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 25-oct-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Mohamed E. Ali (STC) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Telefonica | Improvements for Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | External | Refund functionality for Payment requests +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Deutsche Telekom | Type representing money values +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Telefonica | Enhancement of Documentation within API OAS yaml +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Telefonica | # Add 404 Exception to other API endpoints that have {paymentId} in API path +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Telefonica | API Spec aligment with Commonalities securitySchemes, security and scopes +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Orange | Align Carrier Billing Event with CloudEvents structure +[Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114) | STC | Identify if the payment is one time payment or recurring payment +[Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) | STC | Reversal API +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | TEF | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | TEF | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97) | Improvements for Carrier Billing. Limited scope to topic of **Enhancement of the look & feel**. Action Point to Pedro to provide info to the WG. Feedback provided and documented in the issue, identifying in main relevant CAMARA API the model with specific object schema is used for specific Exceptions. Therefore, adopting this model in Carrier Billing as well. Agreed by the WG and it will be **integrated in next PR**. +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | This feature will be addressed later, after having consistent 1-STEP and 2-STEP Payment models. +[Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105) | Telefónica provides internal analysis, indicating current billing systems works naturally with "decimals", so this model would have huge impact. Orange thinks the same, will check internally for confirmation.
                                                        Nevertheless the issue points the topic of addressing 3 decimals in some currencies/countries, so we need to redefine `amount` model to have 3 digits to cover some UC (i.e. worldwide interoperability). This can be done by indicating `multipleOf: 0.001` in `amount` format as this concept in OAS3 indicates the step between two consequent values, so up to 3 decimal digits can be addressed (NOTE that 5,450 is equal to 5,45 OR 6,000 is equal to 6, as float covers integers per definition). In addition to that, an implementation could specifically throw error if they manage 0, 1 or 2 decimal. Agreed on this way forward. It will be **integrated in the next PR**. +[Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108) | Dealing with two Commonalities topics alignment:
                                                        • **securitySchema**: mention to openId connect could be done in the yaml with the notice that this is not yet completely validated. Discussion ongoing in Commonalities and Identity&Consent Management.
                                                        • **scopes**: scope will be **integrated in the next PR**. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Issue commented during last meeting. Pedro comments besides indicating page, perPage default values in API spec, it makes sense to have an exception to manage uncoherent situations from API Server side (invalid params combination). Ludovic nuances the comment was not about wrong combination but to send an exception when too many record matches, and it will provide feedback within the issue. Discussion continues in the Issue before taking next steps. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | So far, potential impacts identified are:
                                                        • Exception 403 Payment Denied for two-step confirmPayment
                                                        • New event for Payment denied.
                                                        However, in order to not missed anything, it is better to detail the status transitions in every scenario (1-STEP and 2-STEP), so we get two objectives:
                                                        • Having an aligned understanding of the status transitions and document it within API. Identify design actions in the API (new events, exceptions,...).
                                                        • Identify whether state machine needs also to be updated.
                                                        Pedro will draft some documentation within the Issue for alignment and discussion. Discussion continues in the Issue before taking next steps. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica comments the issue in order to indicate the feature of retrieve payment(s) refer to the context of a given phone number. Orange comments there are also Use Cases where API client (App) can obtain information not on behalf of a given user phone number. In API there is no phone number as parameter. This topic requires more discussion and aligment. Comments are welcome for the next meeting. +[Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112) | Agreed by the team. It will be **integrated in the next PR**. +[Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114) | Initial discussion during the meeting. STC comments the issue indicating it has both business and security implications:
                                                        • For recurring payment the OTP will not be required.
                                                        • Security perspective, having impact in Token lifetime.
                                                        Orange indicates this process is managed first with the creation of a product order that represents the subscription and after that, periodical post payments are performed.
                                                        Telefonica indicates probably the Business view on this procedure may be different in Telco Operators so an aligment from Product Perspective is probably required in GSMA OGW product track to have guidance on this matter. +[Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) | Issue introduced during last meeting. Telefonica has commented internally to Business due to the relationship with Refund procedure, as they are elaborating the refunds requirements. In the same fashion as former issue, it is probably required an alignment in GSMA OGW product track to have guidance on this matter. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Not covered in the meeting. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | Not covered in the meeting. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 8th-November 16:00 - 17:00 (CEST)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08.md new file mode 100644 index 0000000000000000000000000000000000000000..91b05be2a7db46836a927db5b0c21a05d4af4901 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-08.md @@ -0,0 +1,44 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 08-nov-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (DEUTSCHE TELEKOM) +- Ludovic Robert (ORANGE) +- Pedro Díez (TELEFONICA) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[PR#120](https://github.com/camaraproject/CarrierBillingCheckOut/pull/120) | Deutsche Telekom | Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Telefonica | Enhancements for Carrier Billing v0.2 - Part I +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | TEF | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | TEF | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#120](https://github.com/camaraproject/CarrierBillingCheckOut/pull/120) | PR triggered by Deutsche Telekom (Rafał) in order to align WG repository with the guidelines of CAMARA regarding [Testing Folder](https://github.com/camaraproject/Template_Lead_Repository/pull/1). Reviewed and approved by Orange and Telefonica. `MERGED` during the meeting. +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Pull Request triggered to cover Issues: [Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97), [Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105), [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106), [Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107), [Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108), [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112). Explained during the meeting the impacts in API yaml spec. Main points covered:
                                                        • Enhance the documentation (from previous documentation & other APIs).
                                                        • Alignment for security scheme & scope. We have distinct scope for create the payment (create), for confirm/cancel in 2 steps (write) and a third (read) for getting the data.
                                                        • Notification alignment with CloudEvents model (QoD/Device Status used as template/references).
                                                        • Added 404 for confirm/cancel payment.
                                                        • Amount precision with 3 decimals.
                                                        Some comments already provided by Ludovic (Orange) and Rafał (Deutsche Telekom) to be managed. They will check/review in deep during the next days. Regarding the point about "x-correlator" it will be managed within Commonalities. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica proposal indicated within the issue is agreed by Orange. Therefore this issue will be **managed in the new next PR**. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Explained the output identified so far in the issue:
                                                        • New event type "denied".
                                                        • New event type "pending_validation" (in the joint anaylisis per [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116)).
                                                        • New Exception 403 CARRIER_BILLING.PAYMENT_DENIED in some operations (this also addresses [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117)).
                                                        Open point: Having a specific attribute for "denied" reason. Work offline to compile common cases.
                                                        Issue will be reviewed by Orange and Deutsche Telekom. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica proposal (approach 1) looks good for Orange. Deutsche Telekom will review offline. It mainly implies documentation but Telefonica (Pedro) will check if additional error should be managed. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Explained the rationale/objective of the issue during the meeting. There may be business scenarios in 2-STEP Payment whether OTP validation procedure is required (because UI associated to OTP validation is built by merchant). Therefore, it is proposed an enhancement in `preparePayment` response regarding validationInfo model and also a new optional method validatePayment. Associated state transitions are also mentioned within the Issue. NOTES:
                                                        • State change lifecycle diagram must be reviewed.
                                                        • (1STEP/2STEP) should be added in all transitions (missing on the first 2).
                                                        Issue will be reviewed offline by Orange and Deutsche Telekom. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | It will be managed with the [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) so as no new exception would be required. +AoB | WG objective:
                                                        • Carrier Billing v0.2.0 Release Candidate will cover all these points handled during today's meeting.
                                                        • Refund & other function will be cover in following release. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 21st-November 11:00 - 12:00 (CET)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21.md new file mode 100644 index 0000000000000000000000000000000000000000..e01d2e1b6079d20672aa30daf5b47ad3a13a4470 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-11-21.md @@ -0,0 +1,44 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-nov-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) +- Benedikt Blome (Vodafone) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Telefonica | Enhancements for Carrier Billing v0.2 - Part I +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | Telefonica | Default values for page and perPage query params in `retrievePayments` endpoint +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Telefonica | Aligment in "transactionOperationStatus" transitions and potential need of new Exception PAYMENT_DENIED +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica | Enhancements in GET payment endpoints +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | Telefonica | [Optional] validate Payment procedure in 2-STEP +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | Telefonica | Business Exception for a given Payment Procedure + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#119](https://github.com/camaraproject/CarrierBillingCheckOut/pull/119) | Pull Request triggered to cover Issues: [Issue#97](https://github.com/camaraproject/CarrierBillingCheckOut/issues/97), [Issue#105](https://github.com/camaraproject/CarrierBillingCheckOut/issues/105), [Issue#106](https://github.com/camaraproject/CarrierBillingCheckOut/issues/106), [Issue#107](https://github.com/camaraproject/CarrierBillingCheckOut/issues/107), [Issue#108](https://github.com/camaraproject/CarrierBillingCheckOut/issues/108), [Issue#112](https://github.com/camaraproject/CarrierBillingCheckOut/issues/112).
                                                        Pull request is `MERGED` so as related issues are `CLOSED`. This is the first of the two PRs in order to reach a stable v0.2.0 version. +[Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109) | WG Agreement for this issue to be **managed in the new next PR**. +[Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) | Impact already identified is aligned:
                                                        • New event type "denied" (probably suitable wording is payment-denied).
                                                        • New event type "pending_validation" (in the joint anaylisis per [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116)).
                                                        • New Exception 403 CARRIER_BILLING.PAYMENT_DENIED in some operations (this also addresses [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117)).
                                                        During meeting open point about "denied" event is aligned and optional parameter to indicate denialReason (string) is agreed to be considered. Then, this issue will be **managed in the next PR**.
                                                        Ludovic (Orange) also comments that currently we have only implicit subscription so adding this denialEvent is fine, but to keep in mind that if we add explicit subscription pattern in future then we can assess event type granularity:
                                                        • Keep event type per state or
                                                        • Have one generic event type for payment state change. +[Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111) | Telefonica proposal approach 1 is seen as better approach. Regarding if additional error should be managed, Pedro (Telefónica) explains the case for FrontEnd Flow (auth_code) -not for Backend Flow (CIBA)- in case we are unable to get the phoneNumber from the access token or if the phoneNumber retrieved from the token is distinct from the one is the payload, so as new 403 Exception is considered (Details in Issue). Ludovic indicates it is fine to consider this case. Then, this issue will be **managed in the next PR**. +[Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116) | This issue was covered in the last meeting. Very small request from Ludovic (Orange) to add (1S/2S) in first 2 transitions diagram clarified during the meeting. Pedro will update source code and image within the issue and will trigger a specific PR for the diagram so as link can be used directly. This issue will be **managed in the next PR**. +[Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117) | It will be managed with the [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110) so as no new exception would be required. +AoB | **WG objective:**
                                                        • Carrier Billing v0.2.0 Release Candidate covering all these points handled during today's meeting.
                                                        • Refund & other function will be cover in following release.

                                                        **Test definition:** Topic commented by Rafał (Deutsche Telekom) and Ludovic (Orange) It will be required to address the test definition in this WG but first need to have a global agreement of the format for the test definition. [Commonalities/Issue#94](https://github.com/camaraproject/Commonalities/issues/94).

                                                        **Test Filtering GET**: Topic commented by Rafał (Deutsche Telekom), [Commonalities/Issue#10](https://github.com/camaraproject/Commonalities/issues/10), [Commonalities/PR#82]([https://github.com/camaraproject/Commonalities/pull/82). Discussion on the filtering criteria, Rafał has prepared a PR in commonalities based on the issue opened. Pedro indicates from Telefónica side it was alignment with Rubén, so as (`gte,gt,lte,lt,eq`) applies for both numeric and dates but no makes sense for enumerated fields (only eq). Rubén also proposed `neq` as the opposite of `eq`. There is some discussion on alignment with TMF pattern (TMF Forum works with URL encoded value of `logical condition` but in CAMARA we are adding suffix to the filtering criteria parameter when applicable. Ludovic raised the point of discrepancy risks between CAMARA & Operate from Channel partner perspective and will also comment in Commonalities issue.

                                                        **Next Steps**: Meeting in 4th December week will be moved to 12th-December (Pedro is on holidays that week) and if needed meeting in 18th December week will be hosted. In the meantime, new PR will be triggered (Pedro) to cover pending points at least during 27th November week in order to have time for its review. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 12th-December 11:00 - 12:00 (CET)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12.md new file mode 100644 index 0000000000000000000000000000000000000000..1702fe30965b21988cb0bd3b0b8191c4818764f8 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-12.md @@ -0,0 +1,36 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 12-dec-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Laurent Grandin (Vodafone) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Telefonica | Enhancements for Carrier Billing v0.2 - Part II +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Pull Request triggered to cover Issues: [Issue#109](https://github.com/camaraproject/CarrierBillingCheckOut/issues/109), [Issue#110](https://github.com/camaraproject/CarrierBillingCheckOut/issues/110), [Issue#111](https://github.com/camaraproject/CarrierBillingCheckOut/issues/111), [Issue#116](https://github.com/camaraproject/CarrierBillingCheckOut/issues/116), [Issue#117](https://github.com/camaraproject/CarrierBillingCheckOut/issues/117).
                                                        Reviewed by Ludovic (Orange). Comment provided regarding the fact in 1-STEP Payment, SYNC behaviour, `denied` status is not reached, so lifecycle diagram needs to be updated. Pedro (Telefonica) agrees on that, because in such a case an exception would be triggered instead. **AP:** Generate a new PR to update lifecycle diagram so as it can be integarted in current [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125). Intention is to have it in this week, therefore to be able to merge it during next week. +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Issue opened by Ludovic (Orange) to deal with Commonalities linting rules track. Rafał (Deutsche Telekom) already explained context in today's Blockchain Public Address WG meeting, so as Pedro (Telefonica) is also aware of that. Assigned to Pedro. Next Commonalities meeting is in 4 weeks, so enough time to check. +AoB | Laurent Grandin (Vodafone) joins WG meeting, he has worked in Carrier Billing/Payment solutions in Vodafone during the last ten years.

                                                        **WG objective:**
                                                        • Carrier Billing v0.2.0 Release Candidate to be generated after [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) merge.

                                                        **Next Features**: Have some slot in the next meeting (20th December) to begin to talk and share views on new features: Refund - [Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104), Recurrent Payments - [Issue#114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114), Reversal procedure - [Issue#115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115) + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 20th-December 15:00 - 16:00 (CET)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20.md new file mode 100644 index 0000000000000000000000000000000000000000..7920f46fb419df9da28fa359667872a3b01f0589 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2023-12-20.md @@ -0,0 +1,38 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 20-dec-2023
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Agustín Martín (Telefonica) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Telefonica | Enhancements for Carrier Billing v0.2 - Part II +[PR#128](https://github.com/camaraproject/CarrierBillingCheckOut/pull/128) |Telefonica | Diagram Payment Lifecycle Adjustment +New Carrier Billing Features | WG | Kick-Off about new Carrier Billing Features + + +### Items Discussion + +Item | Discussion +---- | ---- +[PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) | Pull Request need final review from the team. Ludovic (ORA) approved it as already reviewed. Please make comments if any. Intended to merge this week. Once this done, Pedro (TEF) will create another issue to create the rc version (The version will be suffixed with -rc). Then Pedro will do a PR with the swagger updated with this version. But merging PR #125 is a prerequisite. Accordingly, Pedro will do a PR with the swagger updated with this version. Final comments can be indicated over this new PR. +[PR#128](https://github.com/camaraproject/CarrierBillingCheckOut/pull/128) | Pull Request generated in order to address Ludovic's comment in [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) about not reaching `denied` status in 1-STEP PAYMENT, SYNC process, already `MERGED`. +New Carrier Billing Features | Discussion for new functionalities. Pedro (TEF) listed them:
                                                        • Refund
                                                        • Recurring payment
                                                        • Reversal (This is for temporary transaction so this is a rollback without any charge to the customer)

                                                        Priorities from the community:
                                                        • For DT, needs to check with product team
                                                        • For Orange, needs to check with product team
                                                        • For STC, needs to check with product team
                                                        • For Telefonica, it is refund

                                                        **Zoom on Refund function** by Agustin (TEF) [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104))
                                                        • Refund could be total or partial.
                                                        • Additional state could be added.

                                                        Initial Comments:
                                                        • Ludovic indicated was not aligned from model to have a ‘same’ resource for both payment/refund. His preference is to have separated resources.
                                                        • Mohamed (STC) has some UC where the payment id is not mandatory in the refund (Merchant is in charge to control de balance/accountability of the transactions). Ajit (ERICSSON) agreed on this. Question raised is: then, how the refund is correlated to the payment? Not necessary, Mohamed explained that this is the difference with reversal whom mandate payment.
                                                        • Agustin explained that in Telefonica the refund must be correlated to one payment (not more than one), but the refund could be less than the initial payment amount, so as it is possible to have several refunds for same payment as long as the sum of the refund did not exceed initial payment amount.

                                                        **Zoom on recurring payment** by Mohamed (STC) [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114))
                                                        • It is explained as a feature to differentiate one-time payment from recurrent ones so as OTP is no required from the subsequent payments. In terms of Backend logic is enable internally a periodic payment without explictly triggering it.

                                                        Initial Comments:
                                                        • On roadmap for TEF (but probably in H2' 24)
                                                        • To be check by DT
                                                        • For Orange, Ludovic will confirm but up to his knowledge a specific entity (product order) is managed for ordering a service with recurring payment. This productOrder is send from merchant to Carrier Billing server. Then payment are triggered from the merchant to the Carrier billing server depending on the periodicity. In the payment the product order is provided as reference.

                                                        **Zoom in Reversal** by Mohamed (STC) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115). Relevant information indicated:
                                                        • From a business flow side very similar to refund. In this case, paymentId is mandatory. It is proposed due to any problem in merchant/Operator side while performing a given payment
                                                        • But very different behavior: It will not be reflected in the invoice and distinct behavior for fee/commission as well as they could be cancelled in this case.

                                                        Next actions commented:
                                                        • Operators to check priorities in order to drive technical work
                                                        • Operators to provide Use Cases within the related issues for better understanding of them. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 10th-January 16:00 - 17:00 (CET)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10.md new file mode 100644 index 0000000000000000000000000000000000000000..014f6fc1657d10048ec9ece024673b5adda4be9a --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-10.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 10-January-2024
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Pedro indicates he cannot attend the issue yet. He is going to generate local branch to perform the configurations as per [camaraproject/Commonalities#110](https://github.com/camaraproject/Commonalities/pull/110). Rafał explains that he has already applied in Device Status WG and identified some issues so far. The WoW is by generating a fork of the repository an testing in the fork as per the manual provided in the PR. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | After merging of second the [PR#125](https://github.com/camaraproject/CarrierBillingCheckOut/pull/125) regarding Carrier Billing Enhancements, this issue is to settle this version as v0.2 Release Candidate. If no comments, the related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) will be merged at the end of this week (12th January). Orange has given their approval. After that, new Issue and PR will be generated for Release Generation. +New Carrier Billing Features | Track for new functionalities:
                                                        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
                                                        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
                                                        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

                                                        Priorities from the community:
                                                        • For DT, it is needed to check with product team
                                                        • For Orange, it is needed to check with product team
                                                        • For STC, it is needed to check with product team
                                                        • For Telefonica, it is refund
                                                        • For Ericsson, as per their experience, it is refund

                                                        Next actions commented:
                                                        • Operators to check priorities in order to drive technical work. Kind reminder will be indicated within the related issues.
                                                        • Operators to provide Use Cases within the related issues for better understanding of them. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 24th-January 16:00 - 17:00 (CET)
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24.md new file mode 100644 index 0000000000000000000000000000000000000000..b5471af4856d05f4a7a53257b26f3146321f0869 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-01-24.md @@ -0,0 +1,35 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 24-January-2024
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Pedro has performed some progress on this. Thank you very much to Rafał's support on this. Using a fork-based approach linter has been tested. Details in [Testing_linter](https://github.com/PedroDiez/CarrierBillingCheckOut/pull/1). Some errors found in API Spec format to be reviewed and corrected prior to generate the Release. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Issue to track the generation of release v0.2.0. Related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) ongoing. Linting output to be applied before approving it and be ready to merge. +New Carrier Billing Features | Track for new functionalities:
                                                        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
                                                        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
                                                        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

                                                        Priorities from the community:
                                                        • For DT, so far it is not settle special focus on this API, so as any way forward is seen OK
                                                        • For Orange, it is needed to check with product team
                                                        • For STC, it is refund (full/partial) as commented in related issue
                                                        • For Telefonica, it is refund
                                                        • For Ericsson, as per their experience, it is refund

                                                        Next actions: Have a checkpoint in the next meeting. +AoB | Ludovic commented offline to Pedro that he is having internal meeting in the same slot until MWC. Commented in slack WG channel to check other options for meetings on 7th and 21th February respectively. Based on that new dates will be provided + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 7th February, 11:00 - 12:00 CET
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07.md new file mode 100644 index 0000000000000000000000000000000000000000..688f9529aa772e6bfbf51678623ab4245ed8fa1f --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-07.md @@ -0,0 +1,43 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 07-February-2024
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Mohammed E. Ali (STC) +- Aziz Abouchi (SFR) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Telefonica | Settle Proposal for Release Candidate - v0.2.0 +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Telefonica | Release v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | Currently focus in two main topics:
                                                        • **Initial Release**: In final steps to deliver initial release (version v0.2.0).
                                                        • **Linter rules**: Progressing well just to check final input from Commonalities PR#110. +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Using a fork-based approach, linter has been tested. Details in [Testing_linter](https://github.com/PedroDiez/CarrierBillingCheckOut/pull/1). Progressing very well in this track with the support of Rafał. Just pending to perform final tests based on latest status of Commonalities PR#110. Maybe some additional PR required to fix API Specification format prior to deliver initial release. +[Issue#130](https://github.com/camaraproject/CarrierBillingCheckOut/issues/130) | Issue to track the generation of release v0.2.0 - `CLOSED`. Related [PR#131](https://github.com/camaraproject/CarrierBillingCheckOut/pull/131) `MERGED`. +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Issue to generate Release v0.2.0 - `CLOSED`. Related PRs [PR#134](https://github.com/camaraproject/CarrierBillingCheckOut/pull/134) and [PR#137](https://github.com/camaraproject/CarrierBillingCheckOut/pull/137) `MERGED`. Pending to check output from Linter and maybe some additional PR required. +New Carrier Billing Features | Track for new functionalities:
                                                        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
                                                        • **Recurring payment** [Identify if the payment is one time payment or recurring payment · Issue #114](https://github.com/camaraproject/CarrierBillingCheckOut/issues/114)
                                                        • **Reversal** (This is for temporary transaction so this is a rollback without any charge to the customer) [Reversal API · Issue #115](https://github.com/camaraproject/CarrierBillingCheckOut/issues/115)

                                                        Priorities from the community:
                                                        • For DT, so far it is not settle special focus on this API, so as any way forward is seen OK
                                                        • For Orange, need to check with product team whether refund or recurrent payments may have more priority. In any case it is OK with the move forward agreed
                                                        • For STC, it is refund (full/partial) as commented in related issue
                                                        • For Telefonica, it is refund
                                                        • For Ericsson, as per their experience, it is refund

                                                        Next actions: Let's begin discussion about refund and maybe we can work with recurrent payments in parallel after Orange's checking. +AoB | Aziz Abouchi (SFR) joints for the first time this WG. Context of the work made within the group explained to him. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 21th February, 16:00 - 17:00 CET
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21.md new file mode 100644 index 0000000000000000000000000000000000000000..eb88a4473def293f39721fedf41e598c4d8184f6 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-02-21.md @@ -0,0 +1,37 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-February-2024
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#126](https://github.com/camaraproject/CarrierBillingCheckOut/issues/126) | Orange | Implement use of linting rule set for Carrier Billing API +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Telefonica | Release v0.2.0 +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Initial Release**: Initial release delivered [Release v0.2.0](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.0).
                                                        • **Linter rules**: Checked Successfully with configuration agreed in Commonalities. +[Issue#133](https://github.com/camaraproject/CarrierBillingCheckOut/issues/133) | Issue to generate Release v0.2.0 - `CLOSED`. Related PRs [PR#134](https://github.com/camaraproject/CarrierBillingCheckOut/pull/134), [PR#137](https://github.com/camaraproject/CarrierBillingCheckOut/pull/137) and [PR#141](https://github.com/camaraproject/CarrierBillingCheckOut/pull/141) `MERGED`. +New Carrier Billing Features | Begin to work on Refund feature in next meetings. Requirements/User Stories to be compiled within Issue
                                                        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104). +AoB |
                                                        • **Linter Rules**: After checking successfully the configuration, new Issue/PR will be triggered to apply within the WG. AP@Pedro Diez.
                                                        • **Release v0.2.0**: Checking internally API Publication in TEF, it has been advised that callback notifications endpoints has the same operationId "paymentNotification" for 1-STEP and 2-STEP generating some problems, so as different name will be given in order to avoid publication topics. This is not functional topic but a format one, so it will be managed as a fix. AP @Pedro Diez to open New Issue and related PR to generate a Fix on the release (v0.2.1). + + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 06th March, 16:00 - 17:00 CET
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06.md new file mode 100644 index 0000000000000000000000000000000000000000..53f8418ba232441e286db08b621f39430cd34e4a --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-06.md @@ -0,0 +1,40 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 06-March-2024
                                                        +**Status:** FINAL + +## Attendees + +- Rafał Artych (Deutsche Telekom) +- Ajit Raghavan (Ericsson) +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[PR#142](https://github.com/camaraproject/CarrierBillingCheckOut/pull/142) | Telefonica | Update CHANGELOG +[PR#145](https://github.com/camaraproject/CarrierBillingCheckOut/pull/145) | Telefonica | Release v0.2.1 +[PR#146](https://github.com/camaraproject/CarrierBillingCheckOut/pull/146) | Telefonica | fix_changelog_redoc_link +New Carrier Billing Features | WG | New Carrier Billing Features track + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Initial Release**: Fix over initial release delivered [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1). Functional Release covering 1-STEP and 2-STEP Payments.
                                                        • **Linter rules**: Checked Successfully with configuration agreed in Commonalities with the support of DT (Rafał). Pending PR to apply to this WG repo. **AP@Pedro Diez**. +[PR#142](https://github.com/camaraproject/CarrierBillingCheckOut/pull/142) | After generation of Release v0.2.0 minor Changelog fix is detected. Approved and `MERGED`. +[PR#145](https://github.com/camaraproject/CarrierBillingCheckOut/pull/145) | Generation of [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1) as a fix managing the fact the two callback endpoints were named with the same `operationId` and this may create publication and code generators issues. Approved and `MERGED`. +[PR#146](https://github.com/camaraproject/CarrierBillingCheckOut/pull/146) | After merging of Release v0.2.1 a minor fix in a API specification link identified. Approved and `MERGED` on 6th March, completing the work for [Release v0.2.1](https://github.com/camaraproject/CarrierBillingCheckOut/releases/tag/v0.2.1). +New Carrier Billing Features | Next Feature to work on:
                                                        • **Refund** [Refund functionality for Payment requests · Issue #104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104)
                                                        • Requirements/User Stories to be compiled within Issue. Telefonica (Pedro) indicates final Business requirements have being received during this week and are under evaluation, commenting in advance full/partial refunds are requested. Main points will be reflected within the Issue. Also Ericsson (Ajit) indicates the support of full/partial refunds as a MUST. Objective is to compile requirements within the issue and begin to discuss in the next meeting the requirements and hopefully a draft proposal

                                                        Orange (Ludovic) is pending checking priority from Business. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 20th March, 16:00 - 17:00 CET
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20.md b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20.md new file mode 100644 index 0000000000000000000000000000000000000000..bbc6efcff9feecb71e7ae033dd05857b781d699e --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/MOM-2024-03-20.md @@ -0,0 +1,34 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 20-March-2024
                                                        +**Status:** FINAL + +## Attendees + +- Ludovic Robert (Orange) +- Pedro Díez (Telefonica) + + +## Goals +Review of Issues/PRs and next steps
                                                        + + +Item | Who | Description +---- | ---- | ---- +WG Status | WG | Highlights of WG status +[Issue#148](https://github.com/camaraproject/CarrierBillingCheckOut/issues/148) | WG | Apply Linter Configuration in Carrier Billing +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | WG | Refund functionality for Payment requests enhancement + + +### Items Discussion + +Item | Discussion +---- | ---- +WG Status | • **Linter rules**: Applied in WG.
                                                        • Begin work about refunds +[Issue#148](https://github.com/camaraproject/CarrierBillingCheckOut/issues/148) | Issue opened to apply Linter rules in Carrier Billing WG repository, set to `CLOSED`. Related [PR#149](https://github.com/camaraproject/CarrierBillingCheckOut/pull/149) approved and `MERGED`. +[Issue#104](https://github.com/camaraproject/CarrierBillingCheckOut/issues/104) | Telefónica comments about the main requirements requested by their business and compiled within the Issue. Also commented during the meeting and include later the requirement of obtaining the balance of a given payment (which amount is not refunded). Some comments and considerations provided by Orange (Ludovic):
                                                        • From Business perspective flow is delegated in Payment Aggregators with deals with the specific details of a given market and latter request in a homogeneous way to the Operator.
                                                        • Even some Operators (e.g. Telefonica case) the amount refunded cannot exceed payment amount, we should not impose that as a general rule for any implementation as it may be business cases where for customer inconveniences, the amount refunded could be higher (e.g. to enforce trustability / fidelization from the customer).
                                                        • With regards to asynchronism, it is asked whether refers to a 2-STEP procedure like payments. It is clarified that not related to a 2-STEP process but to design the solution to work with notifications as refund procedure could take some time before being committed.
                                                        • Regarding API design, Orange comments about other option to model endpoint(s) in a way refering to the payment involved in the path: `/payments/{paymentId}/refunds`. + + +### Next Steps +- Next Meetings:
                                                        + • Next meeting: 3rd April, 16:00 - 17:00 CET
                                                        diff --git a/original/CarrierBillingCheckOut/documentation/MeetingMinutes/README.MD b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..6a861e0a28cd082304e853aa11c5318b98afdb18 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/MeetingMinutes/README.MD @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since 3rd April WG Meeting, meeting minutes are placed in [CAMARA Carrier Billing WG Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/sp-cbc+Meeting+Minutes) diff --git a/original/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction.md b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction.md new file mode 100644 index 0000000000000000000000000000000000000000..5f62922ef0f9f294844c70edcaf5e6f7e5e72eae --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/Carrier_API_contribution_introduction.md @@ -0,0 +1,33 @@ + + +# Document objective + +The following document provide a quick introduction of the Orange contribution for a Carrier Billing API + +# Use Case Definition + +The API swagger proposal covers sequence diagram illustrated in supportingDocument folder + + + +Note: +The API allows to manage : + +- a one-step payment (the request is a request to 'execute' a payment) or +- a 2-steps payment - in this case the first step is a payment preparation request that must be later conformed in order to be 'executed. It is possible to cancel a payment preparation. +- retrieve payment by id +- search payment from criterias + + +# API definition + +The proposed API did not features 'purchase' resource management. The purchase could be handeld separatly in another API +The purchase id could be referred in the payment (via referenceCode or via an explicit attribute to be added). + +In order to keep consistence with operator existing assets, the API resource model is directly design from standard RESTful Network API for Payment from the Open Mobile Alliance. + +# API open points + +- use of an explicit attribute to identify the msisdn 'to be charged' (to put right, to identyfy the account which must be charged. This account is identified via the msisdn linked to the account). +- The API could be simplified (for example remove resourceURL, serverReferenceode, etc...atributes if not relevant for our UC) +- Payment lifecyle must be disccussed - OMA could be used as proposal and simplified diff --git a/original/CarrierBillingCheckOut/documentation/SupportingDocuments/README.MD b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..38efecab2903648866bb8d5f867fab0e77ea71c6 --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout.yaml b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f49001d10872ee63080709aa619af8052749816f --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_checkout.yaml @@ -0,0 +1,1062 @@ +openapi: 3.0.3 +info: + title: Carrier Billing Checkout + description: |- + Service that provides functionality for enabling the purchase and payment of goods against OB carrier billing systems. + + # Relevant Definitions and concepts + + - **Purchase**: The action of acquiring a good, service or product. + - **Payment**: The act or process of paying for that good, service or product. + - **Payable**: The concept, service or good a client is paying for. + + # API functionality + + This API allows to create and pay purchases of several Payables. Initial scope is focused in the purchase of digital goods via OB carrier billing systems. + + # Resources and Operations overview + + There are 2 resources in the API: + - The first one, **Purchases**, exposes two operations that allow to create and retrieve purchase info for a specific user. The unique supported **payable** so far is: + - **Digital Good:** Good that the user will acquire, provided by a third party (not the OB) (e.g.: purchase "extra" credit in online gaming, transport tickets, etc). + + - **Payments** is the second one and it exposes four operations to **request the payment** of a specific purchase via OB carrier billing systems **in one-step** (payment request) **or two-step** (payment preparation, payment confirmation or payment cancellation): + - **Carrier Billing:** It means that the operator will perform the billing, accordingly to the user's configuration in the OB; usually this implies that the purchase will be included in the user invoice and then charged to the user, but actually other options may eventually happen, like charge against user prepay balance or other. Notice that this option do not explicitly define the actual payment method, but means that the carrier will be doing the charge based on configuration out of scope of this API. + + - The last resource is **Purchase Notifications**. This resource has one operation to send events to the `notification_url`, when provided by the API client in the purchase creation. + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-write + - carrier-billing-checkout-purchase-digital-good-user-read + - carrier-billing-checkout-payment-user-write + - carrier-billing-checkout-user-notifications +servers: + - url: "{apiRoot}/{basePath}" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: carrier-billing-checkout/v0 + description: Base path for the Carrier Billing Checkout API +paths: + /purchases: + post: + tags: + - Purchases + summary: Creates a new purchase + description: Creates a new Purchase for a given payable + operationId: createPurchase + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Creates a new purchase + content: + application/json: + schema: + $ref: "#/components/schemas/CreatePurchase" + required: true + callbacks: + notifications: + "{$request.body#/notificationUrl}/notifications": + $ref: "#/paths/~1notifications" + responses: + "201": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Purchase created + content: + application/json: + schema: + $ref: "#/components/schemas/PurchaseCreated" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + RegulationTransactionAmountOverpassed: + summary: Purchase amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PURCHASE_AMOUNT_OVERPASSED + message: "Purchase amount overpasses applicable regulation" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + get: + tags: + - Purchases + summary: Retrieve a list of purchases + description: Obtain the list of purchases performed. If no pagination is indicated, list of purchases performed in the last 24 hours are returned. + operationId: getPurchases + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-read + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/Page' + - $ref: '#/components/parameters/PerPage' + - $ref: '#/components/parameters/Seek' + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Content-Last-Key: + $ref: '#/components/headers/Content-Last-Key' + X-Total-Count: + $ref: '#/components/headers/X-Total-Count' + description: Contains information about a list of purchases + content: + application/json: + schema: + $ref: "#/components/schemas/Purchases" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}: + get: + tags: + - Purchases + summary: Retrieve Purchase Information + description: Get Purchase Information of a given payable + operationId: getPurchaseInfo + security: + - three_legged: + - carrier-billing-checkout-purchase-digital-good-user-read + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Contains information about a given purchase + content: + application/json: + schema: + $ref: "#/components/schemas/PurchaseInfo" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment: + post: + tags: + - Payments + summary: Creates a new Payment for a given payable in one-step + description: Creates a new Payment Procedure for a given payable. Once this operation is successful, payment process is triggered and no further action is required, that is, no other payment attempt must be done over the same purchaseId (error code 409 will be triggered). In case a payment attempt over a specific purchaseId ends with error, a new one attempt is allowed with the same conditions. + operationId: createPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + requestBody: + description: Request a new Payment + content: + application/json: + schema: + $ref: "#/components/schemas/RequestPayment" + required: true + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Performed + content: + application/json: + schema: + $ref: "#/components/schemas/PaymentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + PhoneNumberRequired: + summary: Phone Number not provided and cannot be obtained from Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PHONE_NUMBER_REQUIRED + message: "Phone Number is required" + PhoneNumberMismatch: + summary: Phone Number provided not matching Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.INVALID_TOKEN_CONTEXT + message: "Phone Number does not match with Authorization context" + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/prepare: + post: + tags: + - Payments + summary: Creates a new Payment for a given payable in two-step + description: Creates a new Payment Procedure for a given payable. Once this operation is successful, payment process is reserved but not completely triggered/fulfilled. A second explicit action is required to confirm or cancel the payment. + operationId: preparePayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + requestBody: + description: Request a new Payment + content: + application/json: + schema: + $ref: "#/components/schemas/RequestPayment" + required: true + responses: + "200": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Triggered + content: + application/json: + schema: + $ref: "#/components/schemas/PreparePaymentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + PhoneNumberRequired: + summary: Phone Number not provided and cannot be obtained from Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.PHONE_NUMBER_REQUIRED + message: "Phone Number is required" + PhoneNumberMismatch: + summary: Phone Number provided not matching Authorization context + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.INVALID_TOKEN_CONTEXT + message: "Phone Number does not match with Authorization context" + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/confirm: + post: + tags: + - Payments + summary: Confirm a Payment + description: Confirms a Payment for a given payable + operationId: confirmPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "202": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Accepted + "401": + $ref: "#/components/responses/Generic401" + "403": + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic403: + summary: Forbidden + value: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + RegulationAccumulatedTransactionAmountOverpassed: + summary: Accumulated Purchases amount overpassed according to applicable regulation + value: + status: 403 + code: CARRIER_BILLING_CHECKOUT.ACCUMULATED_PURCHASE_AMOUNT_OVERPASSED + message: "Accumulated Purchases Amount overpasses applicable regulation" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic409: + summary: Conflict + value: + status: 409 + code: ALREADY_EXISTS + message: "Another payment confirmation or cancellation has been triggered for the same purchase" + PaymentAlreadyReachedFinalStatus: + summary: Payment already reached a final status for the purchase + value: + status: 409 + code: CARRIER_BILLING_CHECKOUT.PAYMENT_REACHED_FINAL_STATUS + message: "Payment already reached a final status. No further actions can be performed" + "412": + $ref: "#/components/responses/Generic412" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /purchases/{purchaseId}/payment/cancel: + post: + tags: + - Payments + summary: Cancel a Payment + description: Cancels a Payment for a given payable + operationId: cancelPayment + security: + - three_legged: + - carrier-billing-checkout-payment-user-write + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: purchaseId + in: path + description: Purchase ID that was obtained from the createPurchase operation + required: true + schema: + $ref: "#/components/schemas/PurchaseId" + responses: + "202": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Payment Cancellation Accepted + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic409: + summary: Conflict + value: + status: 409 + code: ALREADY_EXISTS + message: "Another payment confirmation or cancellation has been triggered for the same purchase" + PaymentAlreadyReachedFinalStatus: + summary: Payment already reached a final status for the purchase + value: + status: 409 + code: CARRIER_BILLING_CHECKOUT.PAYMENT_REACHED_FINAL_STATUS + message: "Payment already reached a final status. No further actions can be performed" + "412": + $ref: "#/components/responses/Generic412" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + /notifications: + post: + tags: + - Purchase Notifications + summary: "Purchase notifications" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Carrier Billing Checkout server will call this endpoint whenever any purchase related event occurs. + operationId: purchaseNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Creates a new purchase Notification + content: + application/json: + schema: + $ref: "#/components/schemas/Notification" + required: true + responses: + "204": + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Successful notification + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + security: + - apiKey: [] +components: + securitySchemes: + three_legged: + type: oauth2 + flows: + authorizationCode: + authorizationUrl: https://auth.example.com/authorize + tokenUrl: https://auth.example.com/token + scopes: + carrier-billing-checkout-purchase-digital-good-user-write: create purchases + carrier-billing-checkout-purchase-digital-good-user-read: read purchases + carrier-billing-checkout-payment-user-write: make payments + carrier-billing-checkout-user-notifications: read notifications + apiKey: + type: apiKey + description: API key to authorize requests + name: apikey + in: query + schemas: + CreatePurchase: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + notificationAuthToken: + type: string + example: "18dfdf79-e29b-41d4-a716-446655440000" + description: Authentication token for callback API endpoint + - additionalProperties: false + PurchaseCreated: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - processing + - succeeded + - failed + - cancelled + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `processing` - ConfirmPayment has been successfully triggered + * `succeeded` - Purchase payment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + * `cancelled` - CancelPayment has been successfully accomplished + notificationAuthToken: + type: string + example: "18dfdf79-e29b-41d4-a716-446655440000" + description: Authentication token for callback API endpoint + required: + - id + - status + additionalProperties: false + PurchaseBase: + type: object + description: Basic Representation of a Purchase Context + properties: + payable: + $ref: '#/components/schemas/PolymorphicPayable' + notificationUrl: + type: string + pattern: '^https:\/\/.+$' + description: Callback URL where service is going to be notified about any event. The received body definition is indicated in _Purchase notifications_ endpoint. + example: https://notifications-service.com/purchases/ + required: + - payable + PolymorphicPayable: + type: object + description: Basic representation of a payable resource/entity. Please refer to the Model to see all possible instances of Payable + properties: + type: + type: string + description: Type of payable + required: + - type + discriminator: + propertyName: type + mapping: + digital_good: "#/components/schemas/DigitalGood" + oneOf: + - $ref: "#/components/schemas/DigitalGood" + DigitalGood: + description: Basic representation of a digital good, including the total sum of all amount of the items. + allOf: + - $ref: '#/components/schemas/PolymorphicPayable' + - $ref: '#/components/schemas/MerchantInfo' + example: + type: digital_good + order: + id: MarketOrder1 + items: + - name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + - name: MarketOrderItemName2 + amount: + value: 40 + currency: EUR + taxIncluded: true + totalAmount: + value: 65 + currency: EUR + taxIncluded: true + merchant: + id: MerchantId1 + name: MerchantName1 + fee: 15.45 + MerchantInfo: + type: object + description: Represents a collection of goods belonging to a external merchant/provider to be paid + properties: + merchant: + $ref: '#/components/schemas/MarketMerchant' + order: + $ref: '#/components/schemas/MarketOrder' + required: + - order + MarketMerchant: + type: object + description: Represents a merchant/provider from external market + properties: + id: + type: string + description: Unique identifier of the merchant + name: + type: string + description: Merchant description + fee: + type: number + format: float + description: Fee percentage for the merchant/provider + required: + - id + example: + id: MerchantId1 + name: MerchantName1 + fee: 15.45 + MarketOrder: + type: object + description: Represents an order from external market + properties: + id: + type: string + description: Unique identifier of the order on the merchant/provider external system. Only provided when relevant from the API client point of view. + items: + type: array + minItems: 1 + items: + $ref: '#/components/schemas/MarketOrderItem' + totalAmount: + $ref: '#/components/schemas/MoneyAmount' + required: + - items + - totalAmount + example: + id: MarketOrder1 + items: + - name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + - name: MarketOrderItemName2 + amount: + value: 40 + currency: EUR + taxIncluded: true + totalAmount: + value: 65 + currency: EUR + taxIncluded: true + MarketOrderItem: + type: object + description: A item from external merchant/provider to be paid during checkout + properties: + name: + type: string + description: Item description provided by external merchant + amount: + $ref: '#/components/schemas/MoneyAmount' + required: + - name + - amount + example: + name: MarketOrderItemName1 + amount: + value: 25 + currency: EUR + taxIncluded: true + MoneyAmount: + type: object + description: Money amount + properties: + value: + type: number + format: float + multipleOf: 0.01 + description: Amount value + currency: + type: string + description: Currency code in which the amount is expressed. ISO 4217 + taxIncluded: + type: boolean + description: true if the amount includes government taxes + default: false + required: + - value + - currency + PurchaseId: + type: string + format: uuid + description: Unique Purchase identifier + PurchaseInfo: + allOf: + - $ref: '#/components/schemas/PurchaseBase' + - type: object + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - processing + - succeeded + - failed + - cancelled + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `processing` - ConfirmPayment has been successfully triggered + * `succeeded` - ConfirmPayment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + * `cancelled` - CancelPayment has been successfully accomplished + paymentCreationDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is created in server database. This is a technical information. Time-offset from UTC may be used to match local OB time. + paymentDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is effectively performed. This is a business information. Time-offset from UTC may be used to match local OB time. + required: + - id + - status + additionalProperties: false + Purchases: + type: array + items: + $ref: '#/components/schemas/PurchaseInfo' + RequestPayment: + type: object + description: Data Type to indicate in payment request, either 1-step or 2-step. + properties: + phoneNumber: + type: string + description: The MSISDN on which the payment will be performed, in E.164 with `+` format. If no indicated, MSISDN has to be obtained from authorization context (i.e. Authorization header), otherwise exception will be raised. + example: + phoneNumber: '+34699999999' + PaymentInfo: + type: object + description: Data Type to indicate payment information + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + description: | + * `succeeded` - Payment has been successfully executed + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + enum: + - succeeded + - failed + required: + - id + - status + PreparePaymentInfo: + type: object + description: Data Type to indicate prepare payment information + properties: + id: + type: string + format: uuid + description: Unique Identifier of the purchase transaction + status: + type: string + enum: + - initialising + - ready_to_confirm + - failed + description: | + * `initialising` - Purchase process is triggered + * `ready_to_confirm` - PreparePayment has been successfully accomplished + * `failed` - Purchase process failed at any step. New purchase needs to be triggered + paymentOtp: + $ref: '#/components/schemas/PaymentOtp' + required: + - id + - status + PaymentOtp: + type: object + description: Data type to provide the necessary information in order to validate an OTP + properties: + validationEndpoint: + type: string + format: uri + description: URL for OTP validation + parameters: + type: object + description: Pairs of key/value for the parameters that have to be submitted as query parameters when calling the validation endpoint + required: + - validationEndpoint + Notification: + type: object + description: Data type with attributes required for generating a Purchase notification + properties: + purchaseId: + type: string + description: Unique Identifier of the purchase transaction + action: + type: string + enum: + - prepare_payment + - confirm_payment + - cancel_payment + description: | + Indication of the action notified by the event. + * `prepare_payment`: Notification about preparePayment procedure + * `confirm_payment`: Notification about confirmPayment procedure + * `cancel_payment`: Notificacion about cancelPayment procedure + status: + type: string + enum: + - succeeded + - failed + description: | + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + + NOTE: Under reception of a notification with failed status, new purchase procedure shall be initiated by API Client, if required. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + paymentDate: + type: string + format: date-time + description: Date, in ISO-8601 extended local date format, when the payment is effectively performed. This is a business information. Time-offset from UTC may be used to match local OB time. + required: + - purchaseId + - action + - status + - description + ErrorInfo: + type: object + required: + - code + - message + - status + properties: + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + status: + type: integer + description: HTTP response status code + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + Page: + name: page + in: query + description: Requested index to indicate the start of the resources to be provided in the response + schema: + type: integer + PerPage: + name: perPage + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + Seek: + name: seek + in: query + description: Index of last result read to create the next/previous number of results. This query parameter is used for pagination in systems with more than 1000 records + schema: + type: integer + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + Content-Last-Key: + description: Indicates the index of the last result provided in the response + schema: + type: integer + X-Total-Count: + description: Indicates the total number of items in the collection (i.e. total purchases performed) + schema: + type: integer + responses: + Generic400: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_ARGUMENT + message: "Schema validation failed at ..." + Generic401: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Unauthorized + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: UNAUTHORIZED + message: "Authorization failed: ..." + Generic403: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + Generic404: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Resource Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: "The specified resource is not found" + Generic409: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: ALREADY_EXISTS + message: "A specified resource duplicate entry found" + Generic412: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Request cannot be executed in the current system state + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 412 + code: FAILED_PRECONDITION + message: "Request cannot be executed in the current system state" + Generic500: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: "Server error" + Generic503: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Service unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: SERVICE_UNAVALIBLE + message: "Service unavailable" + Generic504: + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + description: Request timeout exceeded + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: "Request timeout exceeded" diff --git a/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment.yaml b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment.yaml new file mode 100644 index 0000000000000000000000000000000000000000..48606cbe33b76bb2faa42f55532201b8bf12313f --- /dev/null +++ b/original/CarrierBillingCheckOut/documentation/SupportingDocuments/carrier_billing_payment.yaml @@ -0,0 +1,1016 @@ +openapi: 3.0.3 +info: + description: Service Enabling Payments against OB Carrier Billing Systems + version: 0.7.0 + title: Carrier Billing Payment + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ +servers: + - url: "{apiRoot}/{basePath}" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: payment/v0 + description: Base path for the carrier billing payment API +paths: + /payments: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - create-payment + tags: + - one-step-payment + summary: Create a new payment for subsequent charging to an end user’s bill + operationId: createPayment + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: '#/components/schemas/CreatePayment' + required: true + responses: + 201: + description: Created + content: + application/json: + schema: + $ref: '#/components/schemas/Payment' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + wrongCurrency: + summary: Currency is unknown or not authorized + value: + code: INVALID_INPUT + status: 400 + message: "Currency is unknown or not authorized: currency" + duplicateClientCorrelator: + summary: clientCorrelator still exist + value: + code: INVALID_INPUT + status: 400 + message: "clientCorrelator already exist on server" + unauthorizedAmount: + summary: unauthorized amount requested + value: + code: INVALID_INPUT + status: 400 + message: "unauthorized amount requested" + 401: + description: Unauthorized + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 403: + description: Forbidden + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 409: + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 500: + description: ServerError + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + 503: + description: Service unavailable + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + get: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - list-payment + tags: + - payment + summary: retrieve payment(s) for subsequent charging to an end user’s bill + operationId: retrievePaymentList + description: retrieve payements based on criteria filtering. + parameters: + - $ref: '#/components/parameters/Fields' + - $ref: '#/components/parameters/Offset' + - $ref: '#/components/parameters/Limit' + responses: + 200: + description: OK + $ref: '#/components/responses/200PaymentArray' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + /payments/{paymentId}: + get: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - retrieve-payment + tags: + - payment + summary: retrieve a payment for subsequent charging to an end user’s bill + operationId: retrievePayment + description: retrieve payement formation for a given payment. + parameters: + - name: paymentId + in: path + description: Payment identifier that was obtained from the create payment operation + required: true + schema: + type: string + responses: + 200: + description: OK + content: + application/json: + schema: + $ref: '#/components/schemas/Payment' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 404: + $ref: "#/components/responses/Generic404" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + 503: + $ref: "#/components/responses/Generic503" + /payments/prepare: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - prepare-payment + tags: + - two-steps-payment + summary: Prepare a new payment procedure for subsequent charging to an end user’s bill + operationId: prepare + requestBody: + description: Amount transaction + content: + application/json: + schema: + $ref: '#/components/schemas/BodyAmountReservationTransactionForReserveInput' + required: true + responses: + 201: + description: Created + content: + application/json: + schema: + $ref: '#/components/schemas/BodyAmountReservationTransactionForReserve' + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + /payments/{paymentId}/confirm: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - confirm-payment + tags: + - two-steps-payment + summary: Confirm or Cancel a reservation on the user’s mobile account + operationId: confirmOrCancel + parameters: + - name: paymentId + in: path + description: The transaction identifier returned when the reservation was + created. + required: true + schema: + type: string + requestBody: + description: capture UnduserId for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/EndUserId" + required: true + responses: + 202: + description: Payment confirmation accepted + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + x-codegen-request-body-name: body + /payments/{paymentId}/cancel: + post: + security: + - oAuth2ClientCredentials: [] + - three_legged: + - cancel-payment + tags: + - two-steps-payment + summary: Cancel a payment preparation on the user’s mobile account + operationId: CancelPayment + parameters: + - name: paymentId + in: path + description: The payment identifier returned when the payment preparation was created. + required: true + schema: + type: string + requestBody: + description: capture UnduserId for payment operation + content: + application/json: + schema: + $ref: "#/components/schemas/EndUserId" + required: true + responses: + 202: + description: Payment Cancellation Accepted + 400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + endUserIdRequired: + summary: end user id is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: endUserId" + paymentIdRequired: + summary: paymentId is required + value: + code: INVALID_INPUT + status: 400 + message: "Expected property is missing: paymentId" + 401: + $ref: "#/components/responses/Generic401" + 403: + $ref: "#/components/responses/Generic403" + 409: + description: Conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: CONFLICT + status: 409 + message: "Another session is created for the same UE" + 500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INTERNAL + status: 500 + message: "Session could not be created" + 503: + $ref: "#/components/responses/Generic503" + x-codegen-request-body-name: body + /notifications: + post: + tags: + - Purchase notifications callback + summary: "Purchase notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Checkout server will call this endpoint whenever any purchase related event occurs. + operationId: purchaseNotification + requestBody: + description: Creates a new purchase Notification + content: + application/json: + schema: + $ref: "#/components/schemas/Notification" + required: true + responses: + "204": + description: Successful notification + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" +components: + schemas: + CreatePayment: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountTransactionInput' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + Payment: + required: + - amountTransaction + - paymentId + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + amountTransaction: + $ref: '#/components/schemas/AmountTransaction' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + paymentCreationDate: + type: string + description: Date when the payment is created in server data base. This is a technical information + format: date-time + paymentDate: + type: string + description: Date when the payment is effectively performed. This is a business information. + format: date-time + AmountTransaction: + required: + - endUserId + - paymentAmount + - referenceCode + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identifies the header that contains the external user token. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForCharge' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + AmountTransactionInput: + required: + - endUserId + - paymentAmount + - referenceCode + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForCharge' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + PaymentAmountForCharge: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + EndUserId: + required: + - endUserId + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided + BodyAmountReservationTransactionForReserve: + required: + - amountTransaction + - paymentId + type: object + properties: + paymentId: + type: string + description: Unique Identifier of the payment + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForReserve' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + BodyAmountReservationTransactionForReserveInput: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForReserveInput' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: Authentification token for callback API + AmountReservationTransactionForReserve: + required: + - endUserId + - paymentAmount + - referenceCode + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForReserve' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + AmountReservationTransactionForReserveInput: + required: + - endUserId + - paymentAmount + - referenceCode + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided. + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForReserve' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + PaymentAmountForReserve: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + BodyAmountReservationTransactionForConfirmOrCancel: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForConfirmOrCancel' + notificationUrl: + type: string + description: Allows asynchronous delivery of purchase related events + BodyAmountReservationTransactionCancel: + required: + - amountTransaction + type: object + properties: + amountTransaction: + $ref: '#/components/schemas/AmountReservationTransactionForConfirmOrCancel' + AmountReservationTransactionForConfirmOrCancel: + required: + - endUserId + - transactionOperationStatus + type: object + properties: + endUserId: + type: string + description: Identify the mobile account to be charged - in general mobile number is provided + clientCorrelator: + type: string + description: Uniquely identifies this create charge request. If there is + a communication failure during the charge request, using the same clientCorrelator + when retrying the request allows the operator to avoid applying the same + charge twice. This field SHOULD be present. + paymentAmount: + $ref: '#/components/schemas/PaymentAmountForConfirmOrCancel' + referenceCode: + type: string + description: Merchant generated payment reference to uniquely identify the + request, for example, in the case of disputes. + transactionOperationStatus: + type: string + description: Specifies the payment status (Processing, Denied, Reserved, + Succeeded, Cancelled). + resourceURL: + type: string + description: URI of the created resource (same as in the Location header) + serverReferenceCode: + type: string + description: Reference to the charge or refund, provided by the server, + and meaningful to the server’s backend system for the purpose of reconciliation. + PaymentAmountForConfirmOrCancel: + required: + - chargingInformation + type: object + properties: + chargingInformation: + $ref: '#/components/schemas/ChargingInformation' + chargingMetaData: + $ref: '#/components/schemas/ChargingMetaData' + amountReserved: + type: number + description: Reserved amount. + totalAmountCharged: + type: number + description: Total amout charged. + ChargingInformation: + required: + - amount + - currency + - description + type: object + properties: + amount: + type: number + description: Amount to be charged or reserved. + currency: + type: string + description: Currency identifier as defined in [ISO4217]. + description: + type: string + description: Description text to be used for information and billing text + ChargingMetaData: + type: object + properties: + onBehalfOf: + type: string + description: Allows aggregators/partners to specify the actual payee. + purchaseCategoryCode: + type: string + description: Indication of the content type. + channel: + type: string + description: Billing policy + isTaxIncluded: + type: boolean + description: if true, the amount is tax included, if false the amount is provided without tax. In both cases, taxAmount could be valued to provide tax amount. + + taxAmount: + type: number + description: The tax amount charged by the merchant. This also provides an indicator to the downstream billing + system. + serviceId: + type: string + description: Billing ID + productId: + type: string + description: Product specification code + ErrorInfo: + type: object + required: + - code + - message + - status + properties: + code: + type: string + description: Code given to this error + status: + type: string + description: HTTP response status code + message: + type: string + description: Detailed error description + Notification: + type: object + description: Data type with attributes required for generating a Payment notification + properties: + paymentId: + type: string + description: Unique Identifier of the payment + action: + type: string + enum: + - prepare_payment + - confirm_payment + - cancel_payment + description: | + Indication of the action notified by the event. + * `prepare_payment`: Notification about preparePayment procedure + * `confirm_payment`: Notification about confirmPayment procedure + * `cancel_payment`: Notificacion about cancelPayment procedure + status: + type: string + enum: + - succeeded + - failed + description: | + Status of the procedure. Possible status are: + * `succeeded`: procedure was accomplished + * `failed`: procedure failed. + NOTE: Under reception of a notification with failed status, new purchase procedure shall be initiated by API Client, if required. + description: + type: string + description: Description of the notification, both used when process was `succeeded` or `failed` indicating in the latter case human understable reason about why process failed. + paymentDate: + type: string + description: Date when the payment is effectively performed. This is a business information. + format: date-time + required: + - paymentId + - action + - status + - description + responses: + Generic400: + description: Invalid input + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: INVALID_INPUT + status: 400 + message: "Schema validation failed at ..." + Generic401: + description: Unauthorized + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: UNAUTHORIZED + status : 401 + message: "Authorization failed: ..." + Generic403: + description: Forbidden + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: FORBIDDEN + status: 403 + message: "Operation not allowed: ..." + Generic404: + description: Resource Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: NOT_FOUND + status : 404 + message: "The specified resource is not found" + Generic500: + description: Server error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: SERVER_ERROR + status: 500 + message: "Server Error" + Generic503: + description: Service unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: SERVICE_UNAVAILABLE + status: 503 + message: "Service unavailable" + Generic504: + description: Request timeout exceeded + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + code: REQUEST_TIMEOUT_EXCEEDED + status: 504 + message: "Request timeout exceeded" + 200PaymentArray: + description: A list of payment(s) + headers: + X-Total-Count: + $ref: '#/components/headers/X-Total-Count' + X-Result-Count: + $ref: '#/components/headers/X-Result-Count' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/Payment' + parameters: + Fields: + name: fields + in: query + description: Comma-separated properties to be provided in response + schema: + type: string + Offset: + name: offset + in: query + description: Requested index for start of resources to be provided in response + schema: + type: integer + Limit: + name: limit + in: query + description: Requested number of resources to be provided in response + schema: + type: integer + headers: + X-Total-Count: + description: Total number of items matching criteria + schema: + type: integer + X-Result-Count: + description: Actual number of items returned in the response body + schema: + type: integer + securitySchemes: + oAuth2ClientCredentials: + type: oauth2 + flows: + clientCredentials: + tokenUrl: '{tokenUrl}' + scopes: {} + BasicAuth: + type: http + scheme: basic + apiKey: + type: apiKey + description: API key to authorize requests + name: apikey + in: query + three_legged: + type: oauth2 + flows: + authorizationCode: + authorizationUrl: https://auth.example.com/authorize + tokenUrl: https://auth.example.com/token + scopes: + payment: perform payment diff --git a/original/ClickToDial/README.md b/original/ClickToDial/README.md new file mode 100644 index 0000000000000000000000000000000000000000..b9edc806828cdadaabcc736504611b1c10cbe5da --- /dev/null +++ b/original/ClickToDial/README.md @@ -0,0 +1,49 @@ +
                                                        + + + + + + + + +# ClickToDial + +Sandbox API Repository to describe, develop, document, and test the ClickToDial Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [Click To Dial](https://lf-camaraproject.atlassian.net/wiki/x/3DHe) + +## Scope +* Service APIs for “Click-To-Dial” +* It provides the API consumer with the ability to: + * establish a voice call between a caller and callee + * terminate an active call + * retrieve the recording of a call (if available) +* Describe, develop, document and test the APIs +* Started: September 2023 + + + + +## Release Information + +> [!NOTE] +> This repository has only pre-release versions available yet. Pre-releases are for testing and may change before public release. + +* The latest pre-release is [r1.2](https://github.com/camaraproject/ClickToDial/releases/tag/r1.2) (release candidate), with the following API versions: + * **click-to-dial 0.1.0-rc.1** + [[YAML]](https://github.com/camaraproject/ClickToDial/blob/r1.2/code/API_definitions/click-to-dial.yaml) [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ClickToDial/r1.2/code/API_definitions/click-to-dial.yaml&nocors) [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ClickToDial/r1.2/code/API_definitions/click-to-dial.yaml) + +* For changes see [CHANGELOG](https://github.com/camaraproject/ClickToDial/tree/main/CHANGELOG) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly (odd weeks), Wednesday, 3 PM CET/CEST (13:00 UTC,21:00 Beijing) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96843390032?password=1153dd0f-f8c8-4d3b-9962-d9685444d145) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/ClickToDial) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ClickToDial/code/API_definitions/click-to-dial.yaml b/original/ClickToDial/code/API_definitions/click-to-dial.yaml new file mode 100644 index 0000000000000000000000000000000000000000..df77766b4d318d95c6b08d2f177298371c656269 --- /dev/null +++ b/original/ClickToDial/code/API_definitions/click-to-dial.yaml @@ -0,0 +1,748 @@ +openapi: 3.0.3 + +info: + title: Click to Dial Service + description: | + The Click to Dial API allows API consumers to initiate and manage voice calls between two parties. The API processes call requests, sets up the call, and provides optional status notifications and call recording features. For specific details, please refer to [click-to-dial_API.md](/documentation/API_documentation/click-to-dial_API.md) + + # API functionality + + Based on the Click-to-Dial API, users can initiate and terminate click-to-call sessions. The Click-to-Call API has the following features: + + * The API consumer calls `POST /calls` to establish a call between the caller and the callee. + * The API consumer calls `DELETE /calls/{callId}` to terminate an active call session. + * Optionally, the API consumer can provide a callback URL (`sink`) to receive status notifications. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: "0.7" + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ClickToDial + +servers: + - url: '{apiRoot}/click-to-dial/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /calls: + post: + tags: + - Calls + summary: Create a new Click to Dial call session + description: | + Creates a new Click to Dial call session between the caller and the callee. + operationId: createCall + security: + - openId: + - "click-to-dial:calls:create" + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Create a Click to Dial call session. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCallRequest' + responses: + '201': + description: Call created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Call" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '409': + $ref: '#/components/responses/Conflict409' + '422': + $ref: '#/components/responses/UnprocessableEntity422' + callbacks: + callStatusChanged: + '{$request.body#/sink}': + post: + summary: Call status changed event + description: | + Event notification delivered to the sink URL when the call status + changes (CloudEvents structured mode). + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/EventCTDStatusChanged' + examples: + CALL_STATUS_CHANGED_EXAMPLE: + $ref: '#/components/examples/CALL_STATUS_CHANGED_EXAMPLE' + responses: + '2XX': + description: Event successfully received by the sink. + /calls/{callId}: + get: + tags: + - Calls + summary: Get call details + description: Retrieve the details and current status of a Click to Dial call session. + operationId: getCall + security: + - openId: + - "click-to-dial:calls:read" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Call details + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Call" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + + delete: + tags: + - Calls + summary: Terminate an active call + description: | + Terminates an active Click to Dial call session identified by the given callId. + operationId: terminateCall + security: + - openId: + - "click-to-dial:calls:delete" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Call terminated + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '409': + $ref: '#/components/responses/Conflict409' + + /calls/{callId}/recording: + get: + tags: + - Recording + summary: Get call recording + description: Retrieve the recording associated with the given callId. + operationId: getRecording + security: + - openId: + - "click-to-dial:recordings:read" + parameters: + - name: callId + in: path + required: true + description: Unique call identifier + schema: + $ref: "#/components/schemas/callId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Call recording resource + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RecordingResource" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + +components: + securitySchemes: + openId: + type: openIdConnect + description: This API uses OpenID Connect for authentication and authorization. + openIdConnectUrl: "https://example.com/.well-known/openid-configuration" + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: '#/components/schemas/XCorrelator' + example: 'b4333c46-49c0-4f62-80d7-f0ef930f1c46' + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for the different services + schema: + $ref: '#/components/schemas/XCorrelator' + example: 'b4333c46-49c0-4f62-80d7-f0ef930f1c46' + + schemas: + XCorrelator: + type: string + pattern: '^[a-zA-Z0-9-_:;./<>{}]{0,256}$' + description: Correlation id for tracking API calls across systems. + + callId: + description: Call identification + type: string + example: 'call_550e8400-e29b-41d4-a716-446655440000' + + Call: + description: Click to Dial call session resource + type: object + properties: + callId: + $ref: '#/components/schemas/callId' + caller: + $ref: '#/components/schemas/Caller' + callee: + $ref: '#/components/schemas/Callee' + status: + $ref: '#/components/schemas/status' + createdAt: + type: string + format: date-time + description: > + Time when the call session was created. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + recordingEnabled: + type: boolean + description: Whether recording is enabled for this call. + required: + - callId + - caller + - callee + - status + - createdAt + + CreateCallRequest: + description: Request to create a new Click to Dial call session + type: object + properties: + caller: + $ref: '#/components/schemas/Caller' + callee: + $ref: '#/components/schemas/Callee' + sink: + $ref: '#/components/schemas/sink' + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + recordingEnabled: + type: boolean + description: Whether call recording is enabled. + required: + - caller + - callee + example: + caller: + number: "+441234567890" + callee: + number: "+441234567891" + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "ya29.A0AR...exampletoken" + accessTokenExpiresUtc: "2026-01-01T00:00:00Z" + accessTokenType: bearer + recordingEnabled: true + + Caller: + type: object + properties: + number: + $ref: '#/components/schemas/PhoneNumber' + required: + - number + + Callee: + type: object + properties: + number: + $ref: '#/components/schemas/PhoneNumber' + required: + - number + + PhoneNumber: + description: Phone number in E.164 format + type: string + pattern: '^\+[1-9]\d{1,14}$' + example: '+12345678' + + sink: + description: The address to which events shall be delivered, using the HTTP protocol. + type: string + format: uri + example: "https://endpoint.example.com/sink" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + description: "The type of the credential. MUST be set to ACCESSTOKEN. Discriminator for credential subtypes." + type: string + enum: + - ACCESSTOKEN + discriminator: + propertyName: credentialType + mapping: + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + required: + - credentialType + + AccessTokenCredential: + description: An access token credential. + type: object + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + credentialType: + description: MUST be `ACCESSTOKEN` for this concrete credential schema. + type: string + enum: + - ACCESSTOKEN + example: ACCESSTOKEN + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: > + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - credentialType + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RecordingResource: + description: Recording file for a Click to Dial call + type: object + properties: + callId: + $ref: '#/components/schemas/callId' + content: + type: string + description: Base64 encoded audio content. + contentType: + type: string + description: MIME type of the audio file. + enum: + - audio/wav + - audio/mp3 + - audio/mpeg + - audio/ogg + generatedAt: + type: string + format: date-time + description: > + Timestamp when the recording was generated. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + required: + - callId + - content + - contentType + + EventCTDStatusChanged: + description: Common attributes of Click to Dial + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + properties: + callId: + $ref: '#/components/schemas/callId' + caller: + $ref: '#/components/schemas/PhoneNumber' + callee: + $ref: '#/components/schemas/PhoneNumber' + status: + type: object + description: | + Call status object. `state` contains the current lifecycle state + and `reason` contains an optional disconnection reason when applicable. + properties: + state: + $ref: '#/components/schemas/status' + reason: + $ref: '#/components/schemas/reason' + required: + - state + recordingResult: + $ref: '#/components/schemas/recordingResult' + callDuration: + $ref: '#/components/schemas/callDuration' + timestamp: + $ref: '#/components/schemas/timestamp' + required: + - callId + - caller + - callee + - status + - timestamp + required: + - data + + status: + description: Call status + type: string + enum: + - initiating + - callingCaller + - callingCallee + - connected + - disconnected + - failed + example: 'callingCaller' + + reason: + description: This field indicates the disconnection reason. This field is mandatory when status is 'disconnected'. + type: string + enum: + - hangUp + - callerBusy + - callerNoAnswer + - callerFailure + - callerAbandon + - calleeBusy + - calleeNoAnswer + - calleeFailure + - other + example: 'hangUp' + + recordingResult: + description: Recording Result. This field is mandatory when recording is enabled and the call is finished. + type: string + enum: + - success + - noRecord + - fail + example: 'success' + + callDuration: + description: This field indicates the duration of the calls, in seconds. This field is mandatory when status is 'disconnected'. + type: string + example: '1600' + + timestamp: + description: > + Time stamp, UTC time. + It must follow RFC 3339 and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + type: string + format: date-time + example: '2017-12-04T18:07:57Z' + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: | + Event compliant with the CloudEvents specification. + Note: Providers MUST deliver events using CloudEvents structured mode + (HTTP header `Content-Type: application/cloudevents+json`). + type: object + properties: + id: + description: Identifier of this event, unique within the event `source` context. UUID is recommended. + type: string + format: uuid + example: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: + description: | + Identifies the context in which an event happened in the Provider implementation. + It SHOULD be an absolute URI identifying the producer (for example the API root or producer instance). + type: string + format: uri-reference + example: https://api.example.com/click-to-dial + type: + description: The type of the event. Use a vendor namespaced event type. + type: string + enum: + - "org.camaraproject.click-to-dial.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.click-to-dial.v0.status-changed: "#/components/schemas/EventCTDStatusChanged" + required: + - id + - source + - specversion + - type + - time + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific syntax exception used when a given field has a pre-defined range or an invalid filter criteria combination is requested. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated. + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + UnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + INVALID_PHONE_NUMBER: + value: + status: 422 + code: INVALID_PHONE_NUMBER + message: Caller or callee number is not a valid E.164 phone number. + SAME_CALLER_CALLEE: + value: + status: 422 + code: SAME_CALLER_CALLEE + message: Caller and callee cannot be the same number. + RECORDING_NOT_SUPPORTED: + value: + status: 422 + code: RECORDING_NOT_SUPPORTED + message: Recording is not supported for this call. + CALLER_NOT_AVAILABLE: + value: + status: 422 + code: CALLER_NOT_AVAILABLE + message: Caller number is currently not reachable or not allowed to start a call. + CALLEE_NOT_AVAILABLE: + value: + status: 422 + code: CALLEE_NOT_AVAILABLE + message: Callee number is currently not reachable or not allowed to receive a call. + + + Conflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + CALL_ALREADY_ACTIVE: + value: + status: 409 + code: CALL_ALREADY_ACTIVE + message: An active call already exists for the given caller and callee. + + examples: + CALL_STATUS_CHANGED_EXAMPLE: + description: | + Call status changed. This example shows a CloudEvent delivered in structured + mode (`Content-Type: application/cloudevents+json`). The `datacontenttype` describes + the `data` payload. + summary: Cloud event example for Click To Dial status change to disconnected due to hangUp + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: https://api.example.com/click-to-dial + specversion: "1.0" + datacontenttype: application/json + type: org.camaraproject.click-to-dial.v0.status-changed + time: 2021-12-12T00:00:00Z + data: + callId: "123e4567-e89b-12d3-a456-426614174000" + caller: "+12345678" + callee: "+12345678" + status: + state: "disconnected" + reason: "hangUp" + recordingResult: "success" + callDuration: "1600" + timestamp: "2017-12-04T18:07:57Z" diff --git a/original/ClickToDial/documentation/API_documentation/click-to-dial_API.md b/original/ClickToDial/documentation/API_documentation/click-to-dial_API.md new file mode 100644 index 0000000000000000000000000000000000000000..de5a080c15d61a1a6d9ee2e81789dcd38f09a944 --- /dev/null +++ b/original/ClickToDial/documentation/API_documentation/click-to-dial_API.md @@ -0,0 +1,321 @@ +# Overview + +The Click to Dial API allows API consumers to initiate and manage voice calls between two parties. The API processes call requests, sets up the call, and provides optional status notifications and call recording features. + +## 1. Introduction + +The Click to Dial API provides a standardized interface to initiate and manage voice call sessions between two parties. It allows API consumers to create a call session, retrieve call status and details, terminate an active call, and retrieve call recordings (if enabled). + + + +## 2\. Quick Start + +### 2.1 Prerequisites + +- **Authentication**: Obtain an OpenID Connect access token from your API provider. + + ```bash + curl -X POST "{openid_token_url}" -d "grant_type=client_credentials&client_id={your_id}&client_secret={your_secret}" + ``` + +### 2.2 Quick Try + +#### 2.2.1 Initiate a Call + +```bash +curl -X POST "{apiRoot}/calls" \ + -H "Authorization: Bearer {access_token}" \ + -H "Content-Type: application/json" \ + -d '{ + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "sink": "https://yourapp.example.com/clicktodialstatusnotify", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "{sink_access_token}", + "accessTokenExpiresUtc": "2025-12-31T23:59:59Z", + "accessTokenType": "bearer" + }, + "recordingEnabled": true + }' +``` + +- **Response:** + +```json +{ + "callId": "123e4567-e89b-12d3-a456-426614174000", + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "status": "initiating", + "createdAt": "2025-12-11T12:00:00Z", + "recordingEnabled": true +} +``` + +#### 2.2.2 Status Notification Callback + +- Implement an HTTP POST endpoint at your provided `sink` URL to receive status notifications. Example payloads are provided in the OpenAPI spec. + +#### 2.2.3 Release a Call + +```bash + curl -X DELETE "{apiRoot}/calls/{callId}" \ + -H "Authorization: Bearer {access_token}" \ +``` + +**Response:** +HTTP 204 No Content + +#### 2.2.4 Download Recording + +```bash +curl -X GET "{apiRoot}/calls/{callId}/recording" \ + -H "Authorization: Bearer {access_token}" \ +``` + +**Response:** + +```json +{ + "callId": "123e4567-e89b-12d3-a456-426614174000", + "content": "BASE64_ENCODED_AUDIO", + "contentType": "audio/wav", + "generatedAt": "2025-12-11T12:05:00Z" +} +``` + +### 2.3 Key Tips + +- **Number Format:** All phone numbers (caller, callee) must be in E.164 format, e.g., "+12345678". +- **Authentication:** Use OpenID Connect; include your access token as a Bearer token. +- **Status Codes:** 201 = created (POST /calls), 200 = success for reads, 204 = no content (DELETE /calls/{callId}), 400 = bad input, 401 = unauthorized, 403 = forbidden, 404 = not found, 409 = conflict, 422 = validation error. +- **Debugging:** Error responses include a code and description/message. + +## 3\. Authentication and Authorization + +This API uses **OpenID Connect** for authentication and authorization. Obtain your access token from your provider and use it in the Authorization header for all API requests. + +## 4\. API Documentation + +### 4.1 API Version + +wip + +### 4.2 Details + +#### 4.2.1 API sequencing + +1. Client calls **POST /calls** to start a call. +2. Server initiates calls to both caller and callee. +3. (Optional) Client may call **DELETE /calls/{callId}** to end a call. +4. Status notifications are sent via HTTP POST to the provided `sink` URL as CloudEvents (structured mode). + +#### 4.2.1 API attributes + +##### Click to Dial Initiation Request + +| Name | Description | Required | Example | +| -------------- | --------------------------------------------------- | -------- | ---------------------------- | +| caller | Calling party number (E.164, with "+") | Yes | "+12345678" | +| callee | Called party number (E.164, with "+") | Yes | "+87654321" | +| sink | (Optional) Callback URL for status notifications | No | `` | +| sinkCredential | (Optional) Callback authentication info (see below) | No | (see below) | + +##### sinkCredential (for `ACCESSTOKEN` type) + +The `SinkCredential` is a discriminator-based object. Currently the only supported `credentialType` is `ACCESSTOKEN` and the concrete `AccessTokenCredential` MUST include the fields below. + +| Name | Description | Required | Example | +| --------------------- | --------------------------------------------- | -------- | ---------------------- | +| credentialType | Must be `ACCESSTOKEN` (discriminator) | Yes | `ACCESSTOKEN` | +| accessToken | Access token used to authenticate event POSTs | Yes | `sink_token` | +| accessTokenExpiresUtc | UTC expiry timestamp for the access token | Yes | `2025-12-31T23:59:59Z` | +| accessTokenType | Token type (OAuth token type) | Yes | `bearer` | + +##### Click to Dial Status Notify (callback payload) + +Status notifications are delivered as CloudEvents (see CloudEvent section below). The `data` payload for `EventCTDStatusChanged` contains the following fields. Note that `status` is now an object containing `state` and optional `reason`. + +| Name | Description | Required | Notes/Values | +| --------------- | -------------------------------------------------------- | -------- | ----------------------------------------------------------------------------- | +| caller | Calling party number (E.164) | Yes | | +| callee | Called party number (E.164) | Yes | | +| status | Object with `state` (lifecycle) and optional `reason` | Yes | `state`: `initiating`,`callingCaller`,`callingCallee`,`connected`,`disconnected`,`failed` | +| status.reason | Disconnection reason (if `state` is `disconnected`) | Cond. | `hangUp`,`callerBusy`,`callerNoAnswer`,`callerFailure`,`callerAbandon`,`calleeBusy`,`calleeNoAnswer`,`calleeFailure`,`other` | +| recordingResult | Recording result when recording enabled | Cond. | `success`,`noRecord`,`fail` | +| callDuration | Duration in seconds (present when call ended) | Cond. | | +| timestamp | UTC timestamp of the event / state change | Yes | RFC 3339 format | +| callId | Identifier of the call (matches the `callId` returned) | Yes | UUID style string | + +#### Release Call + +- Call identifier is provided as a path parameter in DELETE `/calls/{callId}`. + +#### Recording Download + +- Call identifier as path parameter in GET `/calls/{callId}/recording`. + +### 4.3 Endpoint Definitions + +| Endpoint | Method | Description | +| ------------------------------------ | ------ | ---------------------------------- | +| /calls | POST | Start a click-to-dial call | +| /calls/{callId} | GET | Retrieve call details | +| /calls/{callId} | DELETE | End (release) a click-to-dial call | +| /calls/{callId}/recording | GET | Download call recording | + +### 4.4 Errors + +Errors follow the standard format: + +```json +{ + "status": 400, + "code": "INVALID_ARGUMENT", + "message": "Client specified an invalid argument, request body or query param." +} +``` + +Reference the [OpenAPI YAML](../../code/API_definitions/click-to-dial.yaml) for exact error codes and descriptions. + +#### 4.4.1 422 — Business error codes (Unprocessable Entity) + +When a request is syntactically correct but semantically invalid, the API returns `422 Unprocessable Entity` with a business `code` describing the error. The following 422 business error codes are defined in the OpenAPI spec: + +| Code | Description | +| ---- | ----------- | +| `INVALID_PHONE_NUMBER` | Caller or callee number is not a valid E.164 phone number. | +| `SAME_CALLER_CALLEE` | Caller and callee cannot be the same number. | +| `RECORDING_NOT_SUPPORTED` | Recording is not supported for this call. | +| `CALLER_NOT_AVAILABLE` | Caller number is currently not reachable or not allowed to start a call. | +| `CALLEE_NOT_AVAILABLE` | Callee number is currently not reachable or not allowed to receive a call. | + +Example 422 response: + +```json +{ + "status": 422, + "code": "INVALID_PHONE_NUMBER", + "message": "Caller or callee number is not a valid E.164 phone number." +} +``` + +Note: Additional common CAMARA error responses may be defined in the `CAMARA_common.yaml` referenced by this API's readiness checklist. Always consult the OpenAPI YAML for the authoritative list. + +## CloudEvent delivery notes + +- Providers MUST send status notifications as CloudEvents in structured mode. The HTTP header must be `Content-Type: application/cloudevents+json`. +- The CloudEvent MUST include the attributes: `id`, `source`, `type`, `specversion`, and `time`. +- The CloudEvent attribute `datacontenttype` MUST be `application/json` for the `data` payload. + +The CloudEvent `data` payload for Click-to-Dial `EventCTDStatusChanged` includes `callId`, `caller`, `callee`, `timestamp` and `status` (where `status` is an object with `state` and optional `reason`). Providers MUST set `datacontenttype` to `application/json`. + +Example CloudEvent (structured mode) — `CALL_STATUS_CHANGED_EXAMPLE` from the OpenAPI spec: + +```json +{ + "id": "83a0d986-0866-4f38-b8c0-fc65bfcda452", + "source": "https://api.example.com/click-to-dial", + + "specversion": "1.0", + "datacontenttype": "application/json", + "type": "org.camaraproject.click-to-dial.v0.status-changed", + "time": "2021-12-12T00:00:00Z", + "data": { + "callId": "123e4567-e89b-12d3-a456-426614174000", + "caller": "+12345678", + "callee": "+12345678", + "status": { + "state": "disconnected", + "reason": "hangUp" + }, + "recordingResult": "success", + "callDuration": "1600", + "timestamp": "2017-12-04T18:07:57Z" + } +} +``` + +Providers SHOULD ensure event `id` uniqueness and may retry delivery on transient failures. When delivering events to a `sink` that requires authentication, use the provided `sinkCredential` (e.g., set `Authorization: Bearer ` for `ACCESSTOKEN`). + +## Call flow (sequence diagram) + +The following sequence diagram shows the typical flow when creating a Click-to-Dial session, delivering events, and terminating the call. This is a logical flow; implementers may optimize or parallelise steps. + +```mermaid +sequenceDiagram + participant Client + participant Provider + participant Caller + participant Callee + participant Sink + + Client->>Provider: POST /calls {caller, callee, sink, sinkCredential} + Provider->>Caller: Place outbound call to caller + Provider->>Callee: Place outbound call to callee + Provider-->>Client: 201 Created {callId, status} + Provider->>Sink: CloudEvent (status: initiating) + Provider->>Sink: CloudEvent (status: connected) + Client->>Provider: DELETE /calls/{callId} + Provider->>Sink: CloudEvent (status: disconnected) +``` + + +### 4.5 Policies + +N/A + +### 4.6 Example Code Snippets + +#### Start a Call + +```bash +curl -X POST "{apiRoot}/calls" \ + -H "Authorization: Bearer {access_token}" \ + -H "Content-Type: application/json" \ + -d '{ + "caller": { "number": "+12345678" }, + "callee": { "number": "+87654321" }, + "sink": "https://yourapp.example.com/clicktodialstatusnotify", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "{sink_access_token}", + "accessTokenExpiresUtc": "2025-12-31T23:59:59Z", + "accessTokenType": "bearer" + } + }' +``` + +#### Release a Call + +```bash +curl -X DELETE "{apiRoot}/calls/{callId}" \ + -H "Authorization: Bearer {access_token}" +``` + +#### Download a Recording + +```bash +curl -X GET "{apiRoot}/calls/{callId}/recording" \ + -H "Authorization: Bearer {access_token}" +``` + +### 4.7 FAQ's + +To be added in future versions. + +### 4.8 Terms + +N/A + +### 4.9 Release Notes + +This section lists release notes for historical versions. +The current version on the main branch is **wip**. + +- **0.1.0-alpha.1** — Initial release (archived). + +## References + +For a full API schema, see [code/API_definitions/click-to-dial.yaml](../../code/API_definitions/click-to-dial.yaml). diff --git a/original/ClickToDial/documentation/API_documentation/click-to-dial_User_Story.md b/original/ClickToDial/documentation/API_documentation/click-to-dial_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..3998b668ca7c0efb42a6e1f7f3b222d144d8d27d --- /dev/null +++ b/original/ClickToDial/documentation/API_documentation/click-to-dial_User_Story.md @@ -0,0 +1,65 @@ +# Click-to-Dial (CTD) API User Story + +| **Item** | **Details** | +| --------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **Summary** | As an application developer, I want to allow API consumers to initiate Click-to-Dial call sessions via the provider API so that two parties (caller and callee) can be connected via a voice call. The API should support call creation, termination, optional recording, and asynchronous status notifications. | +| **Roles, Actors and Scope** | **Roles:** API consumer; **Actors:** Application developers, integration engineers, CSP (service provider); **Scope:** Create and remove CTD session resources (calls), receive status notifications and retrieve recordings when available. | +| **Pre-conditions** | The client application has been onboarded and is authorized to call the API (has a valid access token with required scopes); the client knows the `apiRoot` and can send HTTP requests; if event delivery is required, the client provides a reachable `sink` URL and optional `sinkCredential`. | +| **Activities / Steps** | Start: Client calls `POST /calls` with `caller`, `callee` and optional `sink`/`sinkCredential`. Flow: Provider places calls to both parties and manages the session; Provider delivers status notifications as CloudEvents to the configured `sink`. End: Client calls `DELETE /calls/{callId}` or session ends normally (call disconnected). | +| **Post-conditions** | Call session resource exists with a `callId` and lifecycle `status`; if `sink` was provided, the provider sends CloudEvents (structured mode) to the `sink` with updates about call state changes; when recording is enabled and the call completes, a recording resource may be available at `GET /calls/{callId}/recording`. | +| **Exceptions** | Authentication/authorization failure (401/403); invalid request body or parameters (400/422); conflicting state when trying to terminate (409); event delivery failures to the `sink` (provider may retry or record failures). | + +## Key implementation details (aligning with API spec) + +- Endpoint naming and behaviour + + - `POST /calls` — create a new CTD call session. Success returns `201 Created` with a `Call` resource body containing `callId`, `caller`, `callee`, `status`, `createdAt`, etc. + - `DELETE /calls/{callId}` — terminate an active call. Returns `204 No Content` when successful. + - `GET /calls/{callId}` — retrieve call details. + - `GET /calls/{callId}/recording` — retrieve recording resource when available. +- Request and response shapes + + - The `CreateCallRequest` expects `caller` and `callee` objects (each with `number` in E.164 format). Optional `sink` (URI) and `sinkCredential` may be provided. Example: + +```json +{ + "caller": { "number": "+441234567890" }, + "callee": { "number": "+441234567891" }, + "sink": "https://example.com/sink", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "ya29.A0AR...", + "accessTokenExpiresUtc": "2026-01-01T00:00:00Z", + "accessTokenType": "bearer" + }, + "recordingEnabled": true +} +``` + +- `SinkCredential` and authentication + + - `SinkCredential` is a discriminator object. Currently the only supported `credentialType` is `ACCESSTOKEN` and the concrete `AccessTokenCredential` MUST include `accessToken`, `accessTokenExpiresUtc` and `accessTokenType`. + - When `sinkCredential` is provided, the provider will use the credential to authenticate HTTP requests to the `sink` when delivering events. The provider should set the `Authorization` header (e.g., `Authorization: Bearer `) when posting events. +- CloudEvents and notifications + + - Providers MUST deliver status notifications as CloudEvents in structured mode (`Content-Type: application/cloudevents+json`). + - The CloudEvent MUST include `id`, `source`, `type`, `specversion`, `time`, and `datacontenttype`. `datacontenttype` for our events is `application/json`. + - The event `data` payload for `EventCTDStatusChanged` contains `callId`, `caller`, `callee`, `timestamp` and `status` (an object): + +```json +"status": { + "state": "disconnected", + "reason": "hangUp" +} +``` + +- `status.state` values: `initiating`, `callingCaller`, `callingCallee`, `connected`, `disconnected`, `failed`. +- `status.reason` is present only when `status.state` is `disconnected` and must be one of the documented disconnection reasons. + +## Example end-to-end + +1. Client POSTs to `/calls` with `caller`, `callee`, optional `sink`/`sinkCredential`. +2. Provider returns `201 Created` with call details including `callId`. +3. Provider sends CloudEvents to `sink` as the call progresses with call status updates. +4. When the call ends, provider sends a final `disconnected` state event including `callDuration` and, if recording was enabled, `recordingResult`. +5. Client can `GET /calls/{callId}/recording` to download the recording resource if available. diff --git a/original/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10.md b/original/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10.md new file mode 100644 index 0000000000000000000000000000000000000000..001601f1558ca0c808703362fe36264de5664d74 --- /dev/null +++ b/original/ClickToDial/documentation/MeetingMinutes/MOM-2024-05-10.md @@ -0,0 +1,35 @@ +# Click to Dial Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) + +* Hanbai Wang (China Mobile) + +* Yu Liu (China Mobile) + +* Shuting Qing (Huawei) + +* Jin Xu (Huawei) + + + +## Agenda +* Discuss the Bi-Weekly Meeting +* Past PR reviews +* Project Timeline + + + +## Discussion + +* The bi-weekly meeting will be scheduled for Friday afternoons every two weeks and will be strictly adhered to in the future. The meeting link will be the Teams connection on the homepage of the click-to-dial subproject team. The weekly meetings will need to discuss unresolved PRs and issues. + +* Firstly, it is clear that all PRs must be discussed in each meeting before they can be merged. After this meeting, the PR with formatting issues mentioned by Herbert needs to be revised and discussed in the next meeting. Only after the discussion and approval can it be merged. The md file format of the Click-to-Dial API user story has significant issues that need to be corrected promptly. The revised version must be discussed in the next meeting. + +* Regarding the project timeline, the current plan is to complete the user story, API definition, API YAML code, and other mandatory documents noted in the checklist by September. Additionally, a deliverable version should be identified. The testing of this API should be completed by the end of this year. + + + + + diff --git a/original/ClickToDial/documentation/MeetingMinutes/README.MD b/original/ClickToDial/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ClickToDial/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ClickToDial/documentation/SupportingDocuments/README.MD b/original/ClickToDial/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ClickToDial/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConnectedNetworkType/README.md b/original/ConnectedNetworkType/README.md new file mode 100644 index 0000000000000000000000000000000000000000..efafae1fc5bd4914e270a7d86830acb7d9bfc8ca --- /dev/null +++ b/original/ConnectedNetworkType/README.md @@ -0,0 +1,60 @@ + + + + + + + + + +# ConnectedNetworkType + +Sandbox API Repository to describe, develop, document, and test the ConnectedNetworkType Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQD1Bg) + +## Scope + +* Service API(s) “ConnectedNetworkType” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * query the the mobile technology of the network that the device is connected to + * receive notifications when the connected network type has changed +* Describe, develop, document, and test the API(s) +* Started: June 2024 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ConnectedNetworkType/releases/tag/r1.2) (Fall25), with the following API versions: + * **connected-network-type-subscriptions v0.2.0** + [[YAML]](https://github.com/camaraproject/ConnectedNetworkType/blob/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type-subscriptions.yaml) + * **connected-network-type v0.2.0** + [[YAML]](https://github.com/camaraproject/ConnectedNetworkType/blob/r1.2/code/API_definitions/connected-network-type.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectedNetworkType/r1.2/code/API_definitions/connected-network-type.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ConnectedNetworkType/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConnectedNetworkType/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ConnectedNetworkType/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions.yaml b/original/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..5110e91a840e937a049ff9f2de34ffcf6b2f01d5 --- /dev/null +++ b/original/ConnectedNetworkType/code/API_definitions/connected-network-type-subscriptions.yaml @@ -0,0 +1,1715 @@ +openapi: 3.0.3 +info: + title: Connected Network Type Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to notifications on changes to the connected network type of a device. + + # Introduction + + ## Connected Network Type Subscription + API consumers can subscribe to receive notifications when the connected network type of a device changes. These notifications are delivered through CloudEvents. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Connected Network Type**: This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`: if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`: if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`: if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`: if device is connected to the 5G network technology + - `UNKNOWN`: if connection technology can not be determined + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type Subscription Management + + These endpoints allow you to manage subscriptions for receiving notifications on changes to the connected network type of a device. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed``: This event is triggered when the connected network type of the device changes. + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + When ``initialEvent`` is set to ``true`` in the subscription request, a notification has to be sent immediately to provide the connected network type of the device targeted. + Note: If the status can not be determined, or if the device is not connected, we send an initial event with ``connectedNetworkType`` valued to`UNKNOWN`. + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding connected network type can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which connected network type notifications should be generated. If the phone number is used as the device identifier when creating a subscription in a multi-SIM scenario, the API may: + - respond with an error, or + - generate network type change notifications for the multi-SIM group as a whole, or + - generate network type change notifications for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ConnectedNetworkType + +servers: + - url: "{apiRoot}/connected-network-type-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Connected Network Type Subscription + description: Operations to manage subscriptions for receiving notifications on changes to the connected network type of a device. + +paths: + /subscriptions: + post: + tags: + - Connected Network Type Subscription + summary: "Create a subscription for receiving notifications on changes to the connected network type of a device" + description: Create a subscription for receiving notifications on changes to the connected network type of a device. + operationId: createConnectedNetworkTypeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The connectivity network type status server will call this endpoint whenever the connected network type of the device changes. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + network-type-changed: + $ref: "#/components/examples/NETWORK_TYPE_CHANGED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created (Successful creation of subscription) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Identifier: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a list of device connected network type event subscription" + description: Retrieve a list of device connected network type event subscription(s) + operationId: retrieveConnectedNetworkTypeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a device connected network type event subscription for a device" + description: retrieve ConnectedNetworkType subscription information for a given subscription ID. + operationId: retrieveConnectedNetworkTypeSubscription + security: + - openId: + - connected-network-type-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Identifier: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connected Network Type Subscription + summary: "Delete connected network type event subscription for a device" + operationId: deleteConnectedNetworkTypeSubscription + description: delete a given ConnectedNetworkType subscription. + security: + - openId: + - connected-network-type-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: ConnectedNetworkType subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ConnectedNetworkType: + type: string + description: Network Type is intended to provide insight to connected network's capabilities from standards perspective. Actual network capabilities may differ based on implementation and MUST be checked with the connected network provider. + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes + subscription-started - Event triggered when the subscription starts + subscription-updated - Event triggered when the subscription is updated + subscription-ended - Event triggered when the subscription is terminated + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-started + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed: "#/components/schemas/EventNetworkTypeChange" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventNetworkTypeChange: + description: event structure for network type change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/EventNetworkTypeChangeData" + + EventNetworkTypeChangeData: + description: Event detail structure for network type changed data events + type: object + required: + - connectedNetworkType + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnded: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + SubscriptionEnded: + description: Event detail structure for SUBSCRIPTION_ENDED event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + NETWORK_TYPE_CHANGED: + description: The cloud event when a connected network type changed + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + specversion: "1.0" + datacontenttype: application/json + data: + subscriptionId: "987654321" + device: + phoneNumber: "+123456789" + connectedNetworkType: 5G + time: "2023-03-22T05:40:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a connected network type subscription ends + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.subscription-ended" + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ACTIVATION_REQUESTED: + description: Subscription details for a subscription whose activation has been requested + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + description: Subscription details for a subscription that has been deleted + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + SUBSCRIPTION_STARTED: + description: The cloud event when a connected network type subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.connected-network-type-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a connected network type subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.connected-network-type-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + description: Subscription details for an active subscription + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + status: ACTIVE + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_IDENTIFIER: + description: Subscription details for an active subscription when a device identifier is also returned + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + status: ACTIVE + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + + CREATE_SUBSCRIPTION: + description: Subscription creation confirmation + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] diff --git a/original/ConnectedNetworkType/code/API_definitions/connected-network-type.yaml b/original/ConnectedNetworkType/code/API_definitions/connected-network-type.yaml new file mode 100644 index 0000000000000000000000000000000000000000..a7012b6783f7d027b338ebb736d15d4ab58ed602 --- /dev/null +++ b/original/ConnectedNetworkType/code/API_definitions/connected-network-type.yaml @@ -0,0 +1,525 @@ +openapi: 3.0.3 +info: + title: Connected Network Type + description: | + This API provides the customer with the ability to query to which Mobile Communication Technology it is connected to. + + # Introduction + + ## Connected Network Type + + The API consumer is able to query the device's connected network type. The API provider can determine this in various ways. For example, the network type can be inferred from the specific radio cell to which the device is connected, as radio cells only support a single technology. It is important to note that the API does not query the device directly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Connected Network Type** : This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`, if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`, if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`, if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`, if device is connected to the 5G network technology + - `UNKNOWN` if connection [technology] can not be determined + + * **LastStatusTime** : This property specifies the time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type + + The endpoint `POST /retrieve` allows to get connected Network Type. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which the connected network type should be returned. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a common connected network type for the multi-SIM group as a whole, or + - return the connected network type for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConnectedNetworkType + +servers: + - url: "{apiRoot}/connected-network-type/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Connected Network Type + description: Operations to get the network type device is connected to +paths: + /retrieve: + post: + tags: + - Connected Network Type + summary: "Get the connected network type" + description: Get the connected network type to which the user device is connected + operationId: getConnectedNetworkType + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - connected-network-type:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeRequest" + required: true + responses: + "200": + description: Contains connected network type + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeResponse" + examples: + Connected To 4G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected To 4G With Device Disambiguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected To 5G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 5G + Connectivity Unknown: + description: Device is not connected to its home mobile network. It may be connected to a different network (e.g. roaming or a WiFi network) or not connected at all. + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: UNKNOWN + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + LastStatusTime: + description: | + The last time that the connected network type status was confirmed to be correct by the API provider. The status should still be valid, but the API provider is unable to confirm this. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ConnectedNetworkTypeResponse: + type: object + required: + - lastStatusTime + - connectedNetworkType + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + + ConnectedNetworkType: + description: | + * UNKNOWN: Used when connection [technology] can not be determined + * 2G: 2nd Generation Mobile Communication Technology + * 3G: 3rd Generation Mobile Communication Technology + * 4G: 4th Generation Mobile Communication Technology + * 5G: 5th Generation Mobile Communication Technology + + type: string + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ConnectedNetworkTypeRequest: + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md b/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..487235b03b9ea5cf4e8e3d43eacdbf11c036929c --- /dev/null +++ b/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for connected-network-type 0.2.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                        public | stable
                                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type.yaml](/code/API_definitions/connected-network-type.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type.feature](/code/Test_definitions/connected-network-type.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/84FlBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md b/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..49184e8f068e7159449079e34f71dd40bbfe37c9 --- /dev/null +++ b/original/ConnectedNetworkType/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for connected-network-type-subscriptions 0.2.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                        public | stable
                                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type-subscriptions.yaml](/code/API_definitions/connected-network-type-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type-subscriptions.feature](/code/Test_definitions/connected-network-type-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/sYFmBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ConnectedNetworkType/documentation/SupportingDocuments/README.MD b/original/ConnectedNetworkType/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConnectedNetworkType/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConnectivityInsights/README.md b/original/ConnectivityInsights/README.md new file mode 100644 index 0000000000000000000000000000000000000000..f80521fcff625d99109db4d53dd8cc1d8985956c --- /dev/null +++ b/original/ConnectivityInsights/README.md @@ -0,0 +1,59 @@ + + + + + + + + + +# ConnectivityInsights + +Sandbox API Repository to describe, develop, document, and test the ConnectivityInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KTLe) + +## Scope +* Service APIs for “Connectivity Insights” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * share key details about their applications that are relevant for network-related decisions across various CAMARA APIs. + * gain visibility into network quality, allowing them to +check if their application's network requirements can be met for a given user session. Based on the API’s response, developers can make informed decisions - like requesting a network boost through CAMARA Quality on Demand API or adjusting application settings (e.g. adjust video resolution) to ensure the best possible user experience. + * enables application developers to receive continuous updates +about network quality through event notifications. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: November 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/ConnectivityInsights/releases/tag/r3.2) (Fall25), with the following API versions: + * **connectivity-insights-subscriptions v0.6.0** + [[YAML]](https://github.com/camaraproject/ConnectivityInsights/blob/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights-subscriptions.yaml) + * **connectivity-insights v0.6.0** + [[YAML]](https://github.com/camaraproject/ConnectivityInsights/blob/r3.2/code/API_definitions/connectivity-insights.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/code/API_definitions/connectivity-insights.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ConnectivityInsights/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConnectivityInsights/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ConnectivityInsights/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Schedule: Bi-weekly on Wednesday at 1500UTC + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vTve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions.yaml b/original/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..9007d9b437d576858d279f2814d07bb3bec6c666 --- /dev/null +++ b/original/ConnectivityInsights/code/API_definitions/connectivity-insights-subscriptions.yaml @@ -0,0 +1,1362 @@ +openapi: 3.0.3 +info: + title: Connectivity Insights Subscriptions + version: wip + x-camara-commonalities: 0.6 + description: | + With CAMARA Connectivity Insights, application developers gain essential + visibility into network quality. This enables them to make informed + decisions that enhance the end-user experience for their applications. + + # Introduction + The Connectivity Insights API allows an application developer to ask + the network the likelihood that an application's networking + requirements can be met for a given end user session. + + This information helps a developer ensure their end users are able to + get the best experience while using the application over their current + network. + + Depending on the answer the network gives, the developer may decide to + request a network boost (via the CAMARA QoD API) , and/or apply + specific changes on the application side e.g. adjusting the + resolution of the video stream upwards or downwards. + + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Identifier for the application server**: + IPv4 and/or IPv6 address of the application server + (application backend) + + * **Notification URL and token**: + Developers may provide a callback URL on which notifications can be + received from the service provider. This is an optional parameter. + + # API functionality + + + Following diagram shows the interaction between different components + ![Sequence Diagram](https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/documentation/API_documentation/ConnectivityInsights-SequenceDiagram.png) + + ### Notification callback + + This endpoint describes the event notification received on subscription + listener side when the event occurred. As for subscription, detailed + description of the event notification is provided in the CAMARA API design + guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as + `POST /{$request.body#/sink}` will be posted by the connectivity insights + resource server to the webhook url provided by notification listener. + + ### Data Minimization + + #### phoneNumber presence: + These rules apply for subscription: + + - If 3-legged access token is used, the POST and GET{id} requests & + responses must NOT provide the ``phoneNumber``. For GET (list) only + subscription(s) for this exactly phone number is/are retrieved (implicit + filtering). + - If 2-legged access token is used, for POST and GET{id}, the presence + of``phoneNumber`` in the request & response is mandatory. For GET (list)the device identifier (``phoneNumber``) could be used as filtering criteria. + + #### sinkCredential presence: + + ``sinkCredential`` is only present in POST request and not provided in + POST or GET response. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + - When the API is invoked using a two-legged access token, the subject will + be identified from the optional `phoneNumber` identifier, which therefore + MUST be provided. + - When a three-legged access token is used however, this optional + `phoneNumber` identifier MUST NOT be provided, as the subject will be + uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged + access token to invoke the API by relying on the information that is + associated with the access token and was identified during the + authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the + optional `phoneNumber` identifier is not included in the request, then the + server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional + `phoneNumber` identifier is also included in the request, then the server + will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This + will be the case even if the same device is identified by these two + methods, as the server is unable to make this comparison. + + # Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/ConnectivityInsights/ + +servers: + - url: "{apiRoot}/connectivity-insights-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Connectivity Insights Subscriptions + description: | + Create and manage a subscription to receive periodic connectivity + insights + +paths: + /subscriptions: + post: + tags: + - Connectivity Insights Subscriptions + description: "Create a Connectivity insights subscription for a device" + summary: "Create a Connectivity insights subscription for a device" + operationId: createSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connectivity-insights-subscriptions:org.camaraproject.connectivity-insights-subscriptions.v0.network-quality:create + + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "Subscription notification callback" + description: | + Important: this endpoint is to be implemented by the API + consumer.The Connectivity Insights server will call this + endpoint whenever a connectivity event occurs that changes + the network's ability to meet the application's demands for + a given device. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json:: + schema: + $ref: "#/components/schemas/CloudEvent" + + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: | + Request accepted to be processed. It applies for async + creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connectivity Insights Subscriptions + summary: "Retrieve a list of apiName event subscription" + operationId: getSubscriptionList + description: | + Operation to list subscriptions authorized to be retrieved by the + provided access token. + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connectivity-insights-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Connectivity Insights Subscriptions + summary: "Operation to retrieve a subscription based on the provided ID" + operationId: getSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - connectivity-insights-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connectivity Insights Subscriptions + summary: "Operation to delete a subscription" + operationId: deleteSubscription + description: Delete a given subscription by ID + security: + - openId: + - connectivity-insights-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: apiName subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: | + Request accepted to be processed. It applies for async deletion + process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authorization for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: | + Subscription identifier that was obtained from the create event + subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + AdditionalKpis: + description: additional information about connectivity quality + type: object + properties: + signalStrength: + description: | + rough indication of the end user device radio signal conditions + type: string + enum: + - excellent + - good + - fair + - poor + - no signal + connectivityType: + description: | + the access technology connecting the user device to the operator + network + type: string + enum: + - 5G-SA + - 5G-NSA + - 4G + - 3G + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: | + The address to which events shall be delivered using the selected + protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + subscriptionId: + type: string + description: | + When this information is contained within an event notification, it SHALL be referred to as `subscriptionId` as per the Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + startsAt: + type: string + format: date-time + description: Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when + `subscriptionExpireTime` is indicated by API client or Telco + Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription + State engine is not mandatory for now. Note not all statuses may + be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is + triggered but subscription creation process is not finished + yet. + - `ACTIVE`: Subscription creation process is completed. + Subscription is fully operative. + - `DEACTIVE`: Subscription is temporarily inactive, but its + workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). + This status applies when subscription is ended due to + `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer + active). This status applies when subscription information is + kept (i.e. subscription workflow is no longer active but its + metainformation is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - DEACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: | + Response for a event-type subscription request managed asynchronously + (Creation or Deletion) + type: object + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: | + When this information is contained within an event notification, it SHALL be referred to as `subscriptionId` as per the Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress":"84.125.93.10", "publicPort":59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: | + Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to + clients. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + + The Operator will use this information to calculate the end to end + network performance in scenarios where its feasible. + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + ApplicationServerIpv4Address: + type: string + example: "192.168.0.1/24" + description: | + IPv4 address may be specified in form
                                                        as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this + exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the + form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. + The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                                                        as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + Config: + description: | + Implementation-specific configuration parameters needed by the + subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, + `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed + event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + description: | + The subscription expiration time (in date-time format) requested by + the API consumer. Up to API project decision to keep it. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated + (>=1) requested by the API consumer - Once this number is reached, + the subscription ends. + Note on combined usage of `initialEvent` and + `subscriptionMaxEvents`: If an event is triggered following + `initialEvent` set to `true`, this event will be counted towards + `subscriptionMaxEvents`. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as + soon as the subscription is created and current situation reflects + event request. + SinkCredential: + type: object + description: | + A sink credential provides authentication or authorization information + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + CreateSubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationServerPorts: + description: | + A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + required: + - device + - applicationProfileId + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: | + The address to which events shall be delivered using the selected + protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + + NetworkQualityInsight: + type: object + description: | + the network's confidence level at being able to meet the network + demands of a given application for a given terminal device. + properties: + papplicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + packetDelayBudget: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinDownstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinUpstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + packetlossErrorRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + jitter: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + additionalKpis: + $ref: "#/components/schemas/AdditionalKpis" + + NetworkQualityThresholdsConfidence: + type: string + description: | + a plain-language indicator of how confident the network is to meet a + given network demand. + enum: + - meets the application requirements + - unable to meet the application requirements + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened, as a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + CloudEvent: + description: The Cloud-Event used for the callback. + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: | + identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: | + Version of the specification to which this event conforms (must be + 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: | + 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + $ref: "#/components/schemas/NetworkQualityInsight" + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connectivity-insights-subscriptions.v0.network-quality: + "#/components/schemas/EventNetworkQuality" + org.camaraproject.connectivityinsights.v0.eventSubscriptionEnded: + "#/components/schemas/EventSubscriptionEnded" + + EventNetworkQuality: + description: event structure for Network Quality + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/NetworkQualityInsight" + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by + the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the + requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by + the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + + EventTypeNotification: + type: string + description: | + event-type - Event triggered when an event-type event occurred + subscription-ended: Event triggered when the subscription ends + enum: + - org.camaraproject.connectivity-insights-subscriptions.v0.network-quality + - org.camaraproject.connectivity-insights-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + event-type - Event triggered when an event-type event occurred + enum: + - org.camaraproject.connectivity-insights-subscriptions.v0.network-quality + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/ConnectivityInsights/code/API_definitions/connectivity-insights.yaml b/original/ConnectivityInsights/code/API_definitions/connectivity-insights.yaml new file mode 100644 index 0000000000000000000000000000000000000000..8476bad00bf7df3e7af8f72f2b5075b6913dd1f9 --- /dev/null +++ b/original/ConnectivityInsights/code/API_definitions/connectivity-insights.yaml @@ -0,0 +1,691 @@ +openapi: 3.0.3 +info: + title: Connectivity Insights + version: wip + x-camara-commonalities: 0.6 + description: | + With CAMARA Connectivity Insights, application developers gain essential + visibility into network quality. This enables them to make informed + decisions that enhance the end-user experience for their applications. + + # Introduction + The Connectivity Insights API allows an application developer to ask + the network the likelihood that an application's networking + requirements can be met for a given end user session. + + This information helps a developer ensure their end users are able to + get the best experience while using the application over their current + network. + + Depending on the answer the network gives, the developer may decide to + request a network boost (via the CAMARA QoD API) , and/or apply + specific changes on the application side e.g. adjusting the + resolution of the video stream upwards or downwards. + + + # API functionality + + Prerequisite: authorisation and authentication + + Usage: + 1. create an application profile using the Connectivity Insights + `application-profiles` API + 2. Request: POST `check-network-quality`, passing the + `applicationProfileId` obtained in step 1, the address/port of an + application server, and at least one device identifier. + 3. Response: The network will indicate whether it can or cannot meet + the application requirements. + 3. Optional: use the `connectivity-insights-subscriptions` API to receive + notifications of network quality. + + Following diagram shows the interaction between different components + ![Sequence Diagram](https://raw.githubusercontent.com/camaraproject/ConnectivityInsights/r3.2/documentation/API_documentation/ConnectivityInsights-SequenceDiagram.png) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/ConnectivityInsights + +servers: + - url: "{apiRoot}/connectivity-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Network Quality + description: | + Read the network's level of confidence that it can meet the quality + thresholds for a given application profile and end user device. + +paths: + /check-network-quality: + post: + security: + - openId: + - connectivity-insights:check + tags: + - Network Quality + summary: Check the network quality. + description: | + Check the network quality. The response shows the network's current + level of confidence that it can meet an application profile's quality + thresholds for a given end user device. + operationId: checkNetworkQuality + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: | + An `ApplicationProfileId` and one or more device identifiers. + Together these allow the network to calculate whether the thresholds + defined in the application profile can be met for the particular + connected device. + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkQualityInsightRequest" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/NetworkQualityInsightResponse" + - $ref: "#/components/schemas/DeviceResponseBody" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + description: Common security scheme for all CAMARA APIs + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkQualityInsightRequest: + description: | + request body to query the network quality for a given device and + application profile + type: object + properties: + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationServerPorts: + description: | + A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + monitoringTimeStamp: + type: string + format: date-time + description: | + this is an optional input parameter. A future data and time can be + provided for predictive data. If no value is provided then the + current date and time is used and network data for the monitoring + data aggregation is used to check network performance against the + application profile defined. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + + NetworkQualityInsightResponse: + type: object + description: the network's confidence level at being able to meet the + network demands of a given application for a given terminal device. + properties: + packetDelayBudget: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinDownstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + targetMinUpstreamRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + packetlossErrorRate: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + jitter: + $ref: "#/components/schemas/NetworkQualityThresholdsConfidence" + additionalKPIs: + $ref: "#/components/schemas/AdditionalKpis" + + AdditionalKpis: + description: additional information about connectivity quality + type: object + properties: + signalStrength: + description: | + rough indication of the end user device radio signal conditions + type: string + enum: + - excellent + - good + - fair + - poor + - no signal + connectivityType: + description: | + the access technology connecting the user device to the operator + network + type: string + enum: + - 5G-SA + - 5G-NSA + - 4G + - 3G + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The + API invoker can provide multiple identifiers to be compatible across + different MNOs. In this case the identifiers MUST belong to the same + device. + NOTE2: for the Commonalities release v0.4, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + optionally prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + DeviceResponseBody: + description: | + The optional device identifier to include in the response + properties: + device: + description: | + The device identifier that was used to fulfil the request. + If this property is not present then the device + identifier sent in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to + clients. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + + The Operator will use this information to calculate the end to end + network performance in scenarios where its feasible. + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + ApplicationServerIpv4Address: + type: string + example: "192.168.0.1/24" + description: | + IPv4 address may be specified in form
                                                        as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this + exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the + form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. + The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                                                        as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + NetworkQualityThresholdsConfidence: + type: string + description: | + a plain-language indicator of how confident the network is to meet a + given network demand. + enum: + - meets the application requirements + - unable to meet the application requirements + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not available for the provided device + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The Service is not available for the provided device. + GENERIC_422_MISSING_IDENTIFIER: + description: + An identifier is not included in the request and the device or phone + number identificationinformation cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist.md b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..d880c30dd2b93ae9d20c506bf28f82eb1203da90 --- /dev/null +++ b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for connectivity-insights v0.6.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                        public | stable
                                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/connectivity-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/ConnectivityInsights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/connectivity-insights.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/K4HWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story.md b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..87fa89bb997e7966fb1c9f11bb5b262af3ca9013 --- /dev/null +++ b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-User-Story.md @@ -0,0 +1,10 @@ +# Connectivity Insights API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to be able to understand my application's network performance demands and determine the likelihood that the network will be able to meet those demands. I can represent my application's network performance demands as a set of metrics (latency, jitter, loss, throughput) and register these with the network using Application Profiles. At runtime, I can query the network to determine if a given device is likely to receive that level of network performance across each metric. In addition, I would like to receive notifications when the network is unable to meet the network performance thresholds for specific device. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
                                                        **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
                                                        **Scope:**
                                                        • Perform network quality check againt the application profile for specific user sessions
                                                        • Create subscriptions to recieve notifications if the network is not able to meet the application's requirements
                                                        | +| ***Pre-conditions*** |The preconditions are listed below:
                                                        1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platfrom.
                                                        2. The API Consumer:BusinessManager has successfully subscribed to the Connectivity Insights product from the product catalog.
                                                        3. The API Consumer:Administrator has onboarded the developer:User to the platform.
                                                        4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                                                        5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:**
                                                          1. The API consumer application server makes a POST request to the check-network-quality endpoint to query if the network can meet the application profile requirements for a specific device.
                                                          2. Optionally, the API consumer application server creates a subscription to receive notifications about network quality changes.

                                                          **Ends when:**
                                                          1. The API endpoint is able to report whether the network can meet the application requirements or not for a given device. or
                                                          2. The monitoring session resource deletion was triggered automatically because the requested duration has expired or the maximum number of events was reached. | +| ***Post-conditions*** | 1. none for synchronous network quality check API.
                                                          2. If subscriptions are created, notifications are sent when network quality changes affect the ability to meet application requirements until the subscription is deleted or has expired.| +| ***Exceptions*** | Several exceptions might occur
                                                          - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                          - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                                                          - Conflict: Internal configuration didn’t allow for operations.
                                                          - Not Found: Requested Application Profile ID or Subscription ID doesn't exist.
                                                          - Session-not-created: Due to other internal errors| diff --git a/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist.md b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..cf5af0508142dfb482a9c92dc5e2498100c6ca39 --- /dev/null +++ b/original/ConnectivityInsights/documentation/API_documentation/connectivity-insights-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for connectivity-insights-subscriptions v0.6.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/connectivity-insights-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/ConnectivityInsights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/connectivity-insights-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/GIBSBQ) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06.md b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06.md new file mode 100644 index 0000000000000000000000000000000000000000..9dbb0de6b7e5ebe9422c07b699fa2a1b2e2b9b05 --- /dev/null +++ b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-06.md @@ -0,0 +1,31 @@ +# Minutes of Connectivity Insights, 6th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +- #3 initial upload of Connectivity Insights YAML +- #4 call schedule + +## Issues +None + +## Discussions +- Administriva (call schedule, need for sub-project to be added to CAMARA wiki) +- Need for API to align with API Design guidelines (initial commit is based on 5GFF) +- Uncertainty regarding consent: who decides whether it is required for this API, the sub-project, The Identity and Consent Project, the TSC, the Stterco? + + +## Actions +- Mahesh to mail the mailing list with call details and update time on GitHub +- Mahesh to align the Connectivity Insights API spec with commonalities guidelines. +- Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. +- Kevin to add Connectivity Insights to CAMARA Wiki + +# AOB + +## Date of next meeting +13th December 2023, 1500 UTC +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13.md b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13.md new file mode 100644 index 0000000000000000000000000000000000000000..f885e73c6e5bb86707f2ea324cbb1fd7d612b2d5 --- /dev/null +++ b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-13.md @@ -0,0 +1,66 @@ +# Minutes of Connectivity Insights, 13th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Santhi Dharmapalan/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Open: +- [#7 Update CAMARA Connectivity Insights API.yaml](https://github.com/camaraproject/ConnectivityInsights/pull/7) fixes [#6](https://github.com/camaraproject/ConnectivityInsights/issues/6) + +Merged since last call: +- #3 initial upload of Connectivity Insights YAML +- #4 call schedule +- #5 update maintainers + +## Issues +Open: +- [#6](https://github.com/camaraproject/ConnectivityInsights/issues/6) API basepath should be human-readable + + This is awaiting confirmation from Herbert that his requested changes are reflected + +- [#9](https://github.com/camaraproject/ConnectivityInsights/issues/9) Performance metric definitions do not match those of the QoD API + + Agreement to adopt the QoD schema. + +## Discussions +- Completed actions were confirmed: + + DONE Mahesh to mail the mailing list with call details and update time on GitHub + + DONE Kevin to add Connectivity Insights to CAMARA Wiki + +- Discussion on whether we need for port identification at both Device and Application port side + + Agreed we would need this for Connectivity Insights between a given device and application server. + The device IPv4 address and public port can be sent by the API consumer, but we will not need to user the private port (pre-NAT) in the API. + The schema deifintions will be reused from QoD. + +- Issues: see discussion and resolution in 'Issues' section above. + +## Actions +Open: +1. Mahesh to align the Connectivity Insights API spec with commonalities guidelines. + - Mahesh will add documentation (similar to QoD) and is going through the API Design Guidelines to align + - Response codes will be adopted from QoD + - we will add cloud notifications in a later release (for now focus is the main API Design guidelines) + +2. Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. + +## AOB + +None + +## Date of next call + +1500 UTC, 1 hour, [Webex link](https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a) + +# AOB + +None + +## Date of next meeting + +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20.md b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20.md new file mode 100644 index 0000000000000000000000000000000000000000..3199ae1234a1c3a230b83fa1e453e2886bf66360 --- /dev/null +++ b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2023-12-20.md @@ -0,0 +1,54 @@ +# Minutes of Connectivity Insights, 20th December 2023 + +## Attendees +- Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +- Syed Rehman/Verizon Wireless +- Santhi Dharmapalan/Verizon Wireless +- Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Merged since last call: +- #7 , #8, #10, #11, 15 + +Open: +- #16 updated documentation to include User Story and API readiness checklist +- - Mahesh has seen the comments and is working on them +- #19 Create Megalinter +- - merged during call + +## Issues +Open: +- #17 Event subscription and notifications should be aligned with API Design Guidelines +- - assigned to Kevin +- #18 Alignment with API design guidelines: add linter +- - fixed by #19 (now merged) + +## Discussions +- Completed actions were confirmed: + + IN PROGRESS Kevin to clarify if a need for consent (or a check for consent-needed) is determined by the sub-project or other body in CAMARA. + + Guidance from commonalities is to include a security component but with an empty scope until this is clarified. + +- Issues: see discussion and resolution in 'Issues' section above. + +- Question: can megalinter be run outside Github (as a precheck)? + +- Labels added to issues and PRs: 0-2-0-wip and 0-3-0-wip. These indicate the target version for the issue/PR (i.e. 'this issue is intended to be fixed in 0-3-0-wip', 'this PR is to create the 0-3-0-wip version' +) +## Actions +Open: +1. Mahesh to align the Connectivity Insights API spec with commonalities guidelines. + - Mahesh will add documentation (similar to QoD) and is going through the API Design Guidelines to align + - Response codes will be adopted from QoD + - we will add cloud notifications in a later release (for now focus is the main API Design guidelines) +2. Kevin to check if megalinter can be run outside Github as a pre-check + +## AOB + +None + +## Date of next meeting +January 3rd 2024 +1500 UTC, 1 hour, [Webex link](https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a) +Online: [Webex meeting link](https://verizon.webex.com/wbxmjs/joinservice/sites/verizon/meeting/download/503bfe52d7524f9bb07d63ebd44cfa30?siteurl=verizon&MTID=mf82f1ec27063f7c14ac189dd72f68c17) diff --git a/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19.md b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19.md new file mode 100644 index 0000000000000000000000000000000000000000..7ff3a59562fbd0fc940ccbc25635a00472dcf278 --- /dev/null +++ b/original/ConnectivityInsights/documentation/MeetingMinutes/MoM-COI-2024-01-19.md @@ -0,0 +1,46 @@ +# Minutes of Connectivity Insights, 19th January 2024 + +## Attendees +* Mahesh Chapalamadugu/Verizon Wireless, 5GFF (CHAIR) +* Kevin Smith/Vodafone (MINUTES) + +## Pull Requests +Merged since last call: +* #22 YAML update following the running of Spectral/Megalinter to fix misalignment with CAMARA guidelines + +Open: +* #16 updated documentation to include User Story and API readiness checklist: +-> Mahesh has seen the comments and is working on them + +## Issues +Open: +* none + +Closed since last call: +* #6, #9, #12, #13, #14, #17, #18, #21 + +## Discussions +* 0-3-0 is almost ready to release, but requires CAMARA consent guidelines to be added (see Action (A3) below) +* We also need to add the Test Definitions. (see Action (A4) below) +* The repo now has 'Discussions' enabled. Kevin has added the Spectral output for the latest YAML commit. +* Kevin will add a discussion on the name of the paths used for the API, as they seem telco-centric and misleading. + +## Actions +Closed: + +~~(A1)Mahesh to align the Connectivity Insights API spec with commonalities guidelines.~~ + +~~(A2)Kevin to check if megalinter can be run outside Github as a pre-check~~ + +New: +* (A3)Kevin will add the consent components and documentation as per [Identity and Consent common guidelines](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md#camara-api-specification---authorization-and-authentication-common-guidelines) +* (A4) Mahesh will investigate developing the Gherkin `.feature` file for test defintions. + +## AOB + +Meetings to now be bi-weekly following as we now have a stable draft API + +## Date of next meeting +January 31st 2024 +1500 UTC, 1 hour, [Webex link]([https://verizon.webex.com/verizon/j.php?MTID=m6daf93460a3b360aebddc23192ff106a](https://eur03.safelinks.protection.outlook.com/?url=https%3A%2F%2Fverizon.webex.com%2Fverizon%2Fj.php%3FMTID%3Dmfd368abae20d28d9ec122b91846fd618&data=05%7C02%7Ckevin.smith%40vodafone.com%7Ce80185de42a74c7b9a0708dc17660ed7%7C68283f3b84874c86adb3a5228f18b893%7C0%7C0%7C638410975421905374%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C41000%7C%7C%7C&sdata=O4mlK0Rvdj2CQY0u36W2A8o9Ld70m9lI2DOBFiReBKA%3D&reserved=0)https://eur03.safelinks.protection.outlook.com/?url=https%3A%2F%2Fverizon.webex.com%2Fverizon%2Fj.php%3FMTID%3Dmfd368abae20d28d9ec122b91846fd618&data=05%7C02%7Ckevin.smith%40vodafone.com%7Ce80185de42a74c7b9a0708dc17660ed7%7C68283f3b84874c86adb3a5228f18b893%7C0%7C0%7C638410975421905374%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C41000%7C%7C%7C&sdata=O4mlK0Rvdj2CQY0u36W2A8o9Ld70m9lI2DOBFiReBKA%3D&reserved=0) + diff --git a/original/ConnectivityInsights/documentation/MeetingMinutes/README.MD b/original/ConnectivityInsights/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConnectivityInsights/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConnectivityInsights/documentation/SupportingDocuments/README.MD b/original/ConnectivityInsights/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConnectivityInsights/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConsentInfo/README.md b/original/ConsentInfo/README.md new file mode 100644 index 0000000000000000000000000000000000000000..b634ab26b253a3b4fdd7f66d978b0e8a670399bb --- /dev/null +++ b/original/ConsentInfo/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# ConsentInfo + +Sandbox API Repository to describe, develop, document, and test the ConsentInfo API(s) within the Working Group [IdentityAndConsentManagement](https://lf-camaraproject.atlassian.net/wiki/x/ZzDe) + +* API Repository [Wiki page](https://lf-camaraproject.atlassian.net/wiki/x/NICeBQ) + + +## Scope + +* Service APIs for “ConsentInfo" (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * **Check the validity of data processing**: The API returns `statusValidForProcessing`, a boolean flag that indicates whether the requested data processing is currently permitted (`true`) or not (`false`). + * **Understand why processing is not allowed**: If data processing is not permitted, the response includes a `statusReason` field to explain why. + * **Retrieve a Capture URL (if requested)**: If the status is not valid because user action is required, and the API Consumer sets `requestCaptureUrl` to `true`, the API will return a `captureUrl` field that can be presented to the User. This URL directs them to the API Provider's secure Consent capture channel, where they can provide or renew their Consent. + + Importantly, this API does NOT delegate Consent capture to the API Consumer but rather empowers the API Consumer to present the API Provider's Consent capture URL at the most opportune time and place. The actual Consent capture occurs within the API Provider's secure environment, ensuring the User's authentication with the API Provider. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* The latest public release is [r2.3](https://github.com/camaraproject/ConsentInfo/releases/tag/r2.3), with the following API versions: + * **consent-info 0.2.0** + [[YAML]](https://github.com/camaraproject/ConsentInfo/blob/r2.3/code/API_definitions/consent-info.yaml) [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ConsentInfo/r2.3/code/API_definitions/consent-info.yaml&nocors) [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ConsentInfo/r2.3/code/API_definitions/consent-info.yaml) + +* The latest public release is always available here: https://github.com/camaraproject/ConsentInfo/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ConsentInfo/releases +* For changes see [CHANGELOG](https://github.com/camaraproject/ConsentInfo/tree/main/CHANGELOG) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings of the working group are held virtually + * Schedule: Every 2 weeks on Wednesdays at 14:00 UTC (IdentityAndConsentManagement Working Group meeting) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94629188836?password=278b4c8a-f370-43bf-bac1-b30a39f169f3) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/lE7e) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ConsentInfo/code/API_definitions/consent-info.yaml b/original/ConsentInfo/code/API_definitions/consent-info.yaml new file mode 100644 index 0000000000000000000000000000000000000000..ce589d249cd75124b40ac24fb7be4791dbf21dab --- /dev/null +++ b/original/ConsentInfo/code/API_definitions/consent-info.yaml @@ -0,0 +1,636 @@ +openapi: 3.0.3 +info: + title: Consent Info + description: | + The Consent Info API allows API Consumers to easily validate whether they have the necessary permissions to process User's personal data for a specific Purpose before using other CAMARA APIs. It provides a simple `true`/`false` response and, when applicable, a URL to direct the User to manage their Consent. + + # Introduction + + This API facilitates compliance with privacy regulations and promotes transparency with Users by providing a standardized way to check whether, for example, the User has given their Consent or opted out of data processing. Key inputs include the specific scope(s) of access being requested (i.e. the CAMARA API(s) operations to which the data processing refers), the Purpose for data processing, and a User identifier (either explicitly provided or derived from a three-legged access token). The API responds with the validity status of the data processing, and, when applicable, can provide a capture URL for the API Consumer to manage it. + + # Relevant terms and definitions + + * **Consent**: An explicit opt-in action that the User takes to allow processing of personal data. Consent grants the API Consumer access to a set of scopes related to the User for a specific Purpose. + * **Purpose**: The reason for which personal data will be processed by an API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + * **Scope**: A string representing the specific access rights or actions an API Consumer requests from the User for their data (e.g., "location-verification:verify"). A request can contain multiple scopes. + + # API Functionality + + This API enables the API Consumer to determine whether their data processing is permitted for a given User, scope(s) and Purpose. + + Specifically, the API: + + * **Provides the data processing validity status**: The API returns `statusValidForProcessing`, a boolean flag that indicates whether the requested data processing is currently permitted (`true`) or not (`false`). + * **Provides an explanation if invalid**: If data processing is not permitted, the response includes a `statusReason` field to explain why. + * **Offers a Capture URL (if requested)**: If the status is not valid because user action is required, and the API Consumer sets `requestCaptureUrl` to `true`, the API will return a `captureUrl` field that can be presented to the User. This URL directs them to the API Provider's secure Consent capture channel, where they can provide or renew their Consent. + * **Supports Callback URL**: The API Consumer can optionally provide a `callbackUrl` when requesting a Consent capture URL. This allows the API Provider to redirect the User back to the API Consumer's specified URL once the Consent capture process is completed, along with the outcome of the process. + + Importantly, this API does NOT delegate Consent capture to the API Consumer but rather empowers the API Consumer to present the API Provider's Consent capture URL at the most opportune time and place. The actual Consent capture occurs within the API Provider's secure environment, ensuring the User's authentication with the API Provider. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared Purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConsentInfo +servers: + - url: "{apiRoot}/consent-info/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Retrieve Status + description: Create a request to retrieve the validity status of the data processing +paths: + /retrieve: + post: + summary: Create a request to retrieve the validity status of the data processing + description: | + Create a request to retrieve the validity status of the API Consumer data processing for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + operationId: retrieveStatus + security: + - openId: + - consent-info:retrieve + tags: + - Retrieve Status + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + description: Retrieve status request + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveStatusRequestBody" + examples: + ONE_SCOPE_ONE_API: + summary: One scope + description: | + Request with one scope corresponding to one API + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + MULTIPLE_SCOPES_ONE_API: + summary: Multiple scopes for one API + description: | + Request with multiple scopes corresponding to one API + value: + phoneNumber: "+123456789" + scopes: + - "quality-on-demand:sessions:create" + - "quality-on-demand:sessions:read" + - "quality-on-demand:sessions:update" + - "quality-on-demand:sessions:delete" + - "quality-on-demand:sessions:retrieve-by-device" + purpose: "dpv:RequestedServiceProvision" + requestCaptureUrl: true + MULTIPLE_SCOPES_MULTIPLE_APIS: + summary: Multiple scopes for multiple APIs + description: | + Request with multiple scopes corresponding to multiple APIs + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + ONE_SCOPE_CALLBACK_URL: + summary: One scope with callback URL + description: | + Request with one scope corresponding to one API including a callback URL + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestCaptureUrl: true + callbackUrl: "https://consumer.example.com/consent/callback" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveStatusResponseBody" + examples: + READY_FOR_PROCESSING: + summary: Ready for processing + description: | + Data processing is allowed for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: true + CONSENT_REQUIRED: + summary: Consent is required + description: | + Consent is required for the requested scope(s) and Purpose + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: REQUESTED + CONSENT_REQUIRED_CAPTURE_URL: + summary: Consent is required and capture URL is provided + description: | + Consent is required for the requested scope(s) and Purpose but it is expired. The API Provider provides a Consent capture URL. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: EXPIRED + expirationDate: "2023-07-03T14:27:08.312+02:00" + captureUrl: "https://example.org/consent-capture-url" + CONSENT_DENIED: + summary: Consent is denied + description: | + Consent is denied for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: DENIED + DATA_PROCESSING_OPT_OUT: + summary: Data processing opt-out + description: | + The User has opted out of the data processing for the requested scope(s) and Purpose. + value: + statusInfo: + - scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: OBJECTED + MULTIPLE_SCOPES_ONE_API: + summary: Multiple scopes for one API + description: | + Request with multiple scopes corresponding to one API. + value: + statusInfo: + - scopes: + - "quality-on-demand:sessions:create" + - "quality-on-demand:sessions:read" + - "quality-on-demand:sessions:update" + - "quality-on-demand:sessions:delete" + - "quality-on-demand:sessions:retrieve-by-device" + purpose: "dpv:RequestedServiceProvision" + statusValidForProcessing: true + MULTIPLE_SCOPES_MULTIPLE_APIS: + summary: Multiple scopes for multiple APIs + description: | + Request with multiple scopes corresponding to multiple APIs. + value: + statusInfo: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: PENDING + - scopes: + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: PENDING + captureUrl: "https://example.org/consent-capture-url" + MULTIPLES_SCOPES_ONE_API_DIFFERENT_STATUS: + summary: Multiple scopes for one API with different status + description: | + Request with multiple scopes corresponding to one API. Different status for each scope. + value: + statusInfo: + - scopes: + - "sim-swap:check" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: true + - scopes: + - "sim-swap:retrieve-date" + purpose: "dpv:FraudPreventionAndDetection" + statusValidForProcessing: false + statusReason: OBJECTED + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/retrieveStatus403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + RetrieveStatusRequestBody: + type: object + description: | + The request body for the retrieve status request. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data, a flag indicating whether the API Consumer requests a Consent capture URL and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - requestCaptureUrl + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + requestCaptureUrl: + type: boolean + description: | + A boolean flag indicating whether the API Consumer requests API Provider to return a Consent capture URL. + * `true` - If set to `true` the API will include a `captureUrl` in the response body if applicable. + * `false` - The API will omit the Consent capture URL from the response. + example: true + callbackUrl: + type: string + format: uri + description: | + Optional URL to which the User shall be redirected by the API Provider once the Consent Capture process has reached a final state (e.g., The User has given their consent). This parameter is only applicable when the API Consumer requests a Consent capture URL by setting `requestCaptureUrl` to `true`. + + The `callbackUrl` parameter enables API Consumers to seamlessly regain control of the user experience once the Consent Capture journey is completed. + + **Functional behaviour** + + When the `callbackUrl` is provided in the request, the API Provider MUST redirect the User to this URL upon completion of the Consent Capture journey. The redirection MUST include a query parameter named `capture_result` that indicates the outcome of the Consent Capture process. The possible values for `capture_result` are: + + - `granted`: The User has successfully provided Consent for the specified scope(s) and Purpose. + - `partial_grant`: The User has provided Consent for only a subset of the originally requested scopes and Purpose. When a `partial_grant` is returned, the API Provider MUST ensure that subsequent API requests reflect the precise subset of scopes actually authorized. + - `denied`: The User has explicitly denied the Consent for the specified scope(s) and Purpose. + - `error`: The Consent Capture flow terminated abnormally due to an internal error, network issue, or unexpected failure. + - `timeout`: The User did not complete the Consent Capture flow within the defined timeout period. + + The API Consumer MAY include a `state` query parameter when initiating the Consent Capture journey (i.e., when opening the Consent Capture URL) to correlate the process with an existing session or transaction context. If the state parameter is provided, the API Provider MUST preserve its value and append it unchanged to the callback URL when redirecting the User at the end of the journey. + + e.g. `https://consumer.example.com/consent/callback?capture_result=granted&state=xyz123` + + **Security considerations** + + - The `callbackUrl` MUST use the `https` scheme to ensure transport security. + Exceptions MAY be allowed for loopback addresses (`http://127.0.0.1`, `http://[::1]`, or `http://localhost`) + or for custom application schemes (e.g., `myapp://consent/callback`) when used as secure deep links + for native applications. + - The `callbackUrl` SHOULD be validated by the API Provider to prevent open redirect or injection attacks. + Validation SHOULD ensure that the domain or scheme is either pre-registered or demonstrably under the + control of the API Consumer. + - The API Provider MUST NOT include any personal data, access tokens, or identifiers in the callback URL. + The `capture_result` parameter MUST be appended, as MUST the `state` parameter if it has been received previously. + - The API Consumer SHOULD validate the origin of incoming callbacks and confirm that the received parameters + correspond to an expected session or flow (e.g., by verifying the `state` value to prevent CSRF attacks). + example: "https://consumer.example.com/consent/callback" + Scopes: + type: array + minItems: 1 + items: + type: string + description: | + List of requested scopes. The scope is a string that represents the access rights that the API Consumer is requesting from the User. + example: + - "location-verification:verify" + Purpose: + type: string + pattern: '^dpv:[a-zA-Z0-9]+$' + description: | + The reason for which personal data will be processed by the API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + example: "dpv:FraudPreventionAndDetection" + RetrieveStatusResponseBody: + type: object + required: + - statusInfo + properties: + statusInfo: + $ref: "#/components/schemas/statusInfo" + captureUrl: + type: string + format: url + description: | + URL where the User can provide the necessary Consent. This field is only present in the API response if the API Consumer requests it and if the following conditions are met: + + - `statusInfo[*].statusValidForProcessing` is `false`, and + - `statusInfo[*].statusReason` is `PENDING`, `REQUESTED` or `EXPIRED`. + + Please note that this field is only applicable when the User Consent is required to enable valid data processing. A unique URL is provided to authorise all items in the statusInfo list that require user action. + example: "https://example.org/consent-capture-url" + statusInfo: + type: array + description: | + Provides information about the validity status of the requested data processing for the specified scope(s) and Purpose. It contains details of whether the processing of the data is currently valid and, if not, the reason why. The expiration date of the validity may be also provided if applicable. + + More than one array item may be required for the requested scope(s) and Purpose, e.g. when the requested scopes relate to multiple APIs. + items: + $ref: "#/components/schemas/statusInfoObject" + minItems: 1 + statusInfoObject: + type: object + required: + - scopes + - purpose + - statusValidForProcessing + properties: + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + statusValidForProcessing: + type: boolean + description: | + Boolean flag that shows the validity status of the requested data processing for the specified scope(s) and Purpose. + * `true` - indicates that the current status is valid and permits the requested data processing. + * `false` - indicates that the requested data processing is not permitted. The reason for this is provided in the `statusReason` field. + statusReason: + type: string + enum: + - PENDING + - REQUESTED + - DENIED + - EXPIRED + - OBJECTED + description: | + This field must be present if `statusValidForProcessing` is `false`. It indicates the reason why the requested data processing is not permitted for the specified scope(s) and Purpose. It provides API Consumers with additional context on the current validity status, helping them to understand its applicability and the next steps they may need to take. + + It is particularly useful for determining whether the API Consumer should prompt the User to take action, such as providing Consent or renewing an existing Consent. + + Possible values are: + + - `PENDING`: The requested data processing has not yet been established or fully validated under the applicable privacy regulations. + For example, the User has not yet provided Consent when it is required. + - `REQUESTED`: The permission for the requested data processing has been submitted but has not yet been granted or confirmed. + This is common when the API Consumer has initiated a request for Consent capture, but the User has not yet completed the process. For example, this occurs when a notice prompting the User to provide Consent has been displayed, but they have not yet made a decision. + - `DENIED`: The User has explicitly refused their permission for the requested data processing. + For example, when the User refuses to grant Consent for the data processing, or when they previously granted Consent but later withdrew it. + - `OBJECTED`: The user has opted out of the requested data processing, despite a previous explicit opt-in not being required. + This is common when the User has exercised their right to object to data processing under the applicable privacy regulations. + - `EXPIRED`: When applicable, the validity of the data processing has ceased due to the passage of time or a pre-defined condition. + This is common for time-limited Consents. + expirationDate: + type: string + format: date-time + description: | + The date and time at which the validity of the data processing is set to expire or has expired. + It applies mainly to time-limited Consents, or other cases where a specific duration of validity is defined for the data processing. This field is only applicable: + + - if `statusValidForProcessing` is `true` (indicating a future expiration), or + - if `statusValidForProcessing` is `false` and `statusReason` is `EXPIRED` (indicating the past expiration date). + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2023-07-03T14:27:08.312+02:00" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + retrieveStatus403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CONSENT_INFO.NOT_ALLOWED_SCOPES_PURPOSE + - CONSENT_INFO.CAPTURE_FREQUENCY_EXCEEDED + - CONSENT_INFO.INVALID_CALLBACK_URL + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + NOT_ALLOWED_SCOPES_PURPOSE: + description: The requested scope(s) and Purpose combination is not allowed for the API Consumer, e.g. the API Consumer has not onboarded the appropriate API(s) with the API Provider for the declared Purpose. + value: + status: 403 + code: CONSENT_INFO.NOT_ALLOWED_SCOPES_PURPOSE + message: The requested scope(s) and Purpose combination is not allowed for this API Consumer. + CAPTURE_FREQUENCY_EXCEEDED: + description: The frequency of consent capture requests has been exceeded. + value: + status: 403 + code: CONSENT_INFO.CAPTURE_FREQUENCY_EXCEEDED + message: The frequency of consent capture requests has been exceeded. Please try again later. + INVALID_CALLBACK_URL: + description: The provided callback URL is invalid. + value: + status: 403 + code: CONSENT_INFO.INVALID_CALLBACK_URL + message: The provided callback URL is invalid. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration diff --git a/original/ConsentInfo/documentation/SupportingDocuments/README.MD b/original/ConsentInfo/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConsentInfo/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConsentManagement/README.md b/original/ConsentManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..4ea137a2ecf423f4574917c47346e35be65bd7ff --- /dev/null +++ b/original/ConsentManagement/README.md @@ -0,0 +1,46 @@ + + + + + + + + + +# ConsentManagement + +Sandbox API Repository to describe, develop, document, and test the ConsentManagement Service API(s) within the Working Group [Identity And Consent Management](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14561383/Identity+Consent+Management). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/WgDDH) + +## Scope + +* Service API(s) “ConsentManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * **Create Consent**: Allows API Consumers to create a new Consent for a User, specifying the requested scope(s) and Purpose. The API Consumer must provide the necessary information to capture the User's Consent. + * **Update Consent**: Enables API Consumers to update an existing Consent and change its status. + * **Retrieve Consent Information**: Allows API Consumers to retrieve information about existing Consents for a User based on specified scope(s) and Purpose. This operation can also return the Consent texts presented to the User during the Consent Capture process if requested. + + It is important to note that the API Provider remains fully responsible for Consent storage, auditing and transparency. Access to this functionality is restricted to trusted API Consumers in accordance with the API Provider's policy. This API only applies to scenarios involving the legal basis of Consent. Scenarios involving a different legal basis for data processing are excluded and would be handled by the API Provider through non-delegated mechanisms. +* Describe, develop, document, and test the API(s) +* Started: December 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: Every 2 weeks on Wednesdays at 14:00 UTC (IdentityAndConsentManagement Working Group meeting) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94629188836?password=278b4c8a-f370-43bf-bac1-b30a39f169f3) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/lE7e) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of the Working Group can be sent using . diff --git a/original/ConsentManagement/code/API_definitions/consent-management.yaml b/original/ConsentManagement/code/API_definitions/consent-management.yaml new file mode 100644 index 0000000000000000000000000000000000000000..b647a88e5d9f4c00584ab3c7aeb10156d275ed31 --- /dev/null +++ b/original/ConsentManagement/code/API_definitions/consent-management.yaml @@ -0,0 +1,956 @@ +openapi: 3.0.3 +info: + title: Consent Management + description: | + This API enables API Consumers to manage User Consents for accessing personal data via CAMARA APIs. It allows creating, updating, and retrieving Consent information based on specific scope(s) and Purpose in the API Provider's Consent Management system. + + # Introduction + + In the context of CAMARA, Consent Management refers to the processes and mechanisms that allow API Consumers to obtain, manage, and verify User Consents for accessing and processing personal data through CAMARA APIs. This API specification defines the operations and data structures necessary for API Consumers to interact with Consent Management services provided by API Providers. + + This optional, controlled delegation model enables trusted API Consumers to capture the User Consent directly within their own applications using Consent texts and parameters provided by API Providers. This model aims to streamline the User Consent capture process, enhance User experience, and ensure compliance with data protection regulations by leveraging API Provider-verified Consent texts. + + # Relevant terms and definitions + + * **Consent**: An explicit opt-in action that the User takes to allow processing of personal data. Consent grants the API Consumer access to a set of scopes related to the User for a specific Purpose. + * **Purpose**: The reason for which personal data will be processed by an API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + * **Scope**: A string representing the specific access rights or actions an API Consumer requests from the User for their data (e.g., "location-verification:verify"). A request can contain multiple scopes. + + # API Functionality + + This Consent Management API provides the following key functionalities: + + - **Create Consent**: Allows API Consumers to create a new Consent for a User, specifying the requested scope(s) and Purpose. The API Consumer must provide the necessary information to capture the User's Consent. + - **Update Consent**: Enables API Consumers to update an existing Consent and change its status. + - **Retrieve Consent Information**: Allows API Consumers to retrieve information about existing Consents for a User based on specified scope(s) and Purpose. This operation can also return the Consent texts presented to the User during the Consent Capture process if requested. + + It is important to note that the API Provider remains fully responsible for Consent storage, auditing and transparency. Access to this functionality is restricted to trusted API Consumers in accordance with the API Provider's policy. This API only applies to scenarios involving the legal basis of Consent. Scenarios involving a different legal basis for data processing are excluded and would be handled by the API Provider through non-delegated mechanisms. + + ## Consent status lifecycle + + A User Consent follows a defined status lifecycle. The possible statuses and their allowed transitions are described below and illustrated in the diagram: + + - **PENDING**: Initial status indicating that the User Consent has not yet been requested from the User. No Consent record (`consentId`) exists at this stage. + - **REQUESTED**: The User Consent has been requested from the User, but the User has not yet responded. A Consent record exists with a `consentId`. + - **GRANTED**: The User has approved the Consent, allowing the requested data processing. This status is set when creating or updating a Consent with status `GRANTED`. + - **DENIED**: The User has rejected the Consent. This status is set when creating or updating a Consent with status `DENIED`. + - **EXPIRED**: The User Consent has expired because its TTL (time-to-live) has been reached. Both `GRANTED` and `DENIED` Consents can expire. The API Provider determines the expiration date based on its internal policies. + + The allowed transitions are: + + - `PENDING/REQUESTED` → `GRANTED`: The User approves the Consent. + - `PENDING/REQUESTED` → `DENIED`: The User rejects the Consent. + - `GRANTED` → `DENIED`: The User revokes a previously granted Consent. + - `DENIED` → `GRANTED`: The User reconsents after previously denying. + - `GRANTED` → `EXPIRED`: The Consent TTL is reached and the Consent expires. + - `DENIED` → `EXPIRED`: The Consent TTL is reached and the Consent expires. + - `EXPIRED` → `GRANTED`: The User renews and approves an expired Consent. It requires the API Consumer to recapture the User Consent and update the Consent status to `GRANTED` via the `updateConsent` operation. + - `EXPIRED` → `DENIED`: The User renews and rejects an expired Consent. It requires the API Consumer to recapture the User Consent and update the Consent status to `DENIED` via the `updateConsent` operation. + + Note that API Consumers can only set a Consent status to `GRANTED` or `DENIED` via the `createConsent` and `updateConsent` operations. The `PENDING`, `REQUESTED`, and `EXPIRED` statuses are managed by the API Provider. + + The following diagram illustrates the allowed status transitions: + + ``` + +-----------------+ + |PENDING/REQUESTED| + +--+------------+-+ + | | + User Rejects User Approves + +--------+ +-------+ + | | + +-----v--------+ +-------v------+ + | <-Revocation-+ | + | DENIED +-Re-consent-> GRANTED | + | +-+ +-+ | + +---^----------+ | | +--------^-----+ + | | | | + | TTL Reached | | + | | | | + | | TTL Reached | + | | | | + Renewed | | Renewed + & Rejected +--v--------v--+ & Approved + | | | | + +---------+ EXPIRED +-------+ + | | + +--------------+ + ``` + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared Purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ConsentInfo +servers: + - url: "{apiRoot}/consent-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Consent Management + description: Operations to manage User's Consent +paths: + /consents: + post: + summary: Create User Consent + description: | + This operation allows the API Consumer to create a Consent for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The API Provider will set the creation date of the User Consent to the current date and time when the `createConsent` operation is invoked successfully by the API Consumer. + + The expiration date of the User Consent created by the API Consumer will be determined by the API Provider's internal policies. The API Consumer cannot set or modify the expiration date of the User Consents captured in a delegated manner. + operationId: createConsent + security: + - openId: + - consent-management:create + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + description: createConsent operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/CreateConsentRequestBody" + examples: + CREATE_CONSENT_REQUEST_GRANTED: + summary: Create Consent request with status GRANTED + value: + phoneNumber: "+123456789" + scopes: + - "number-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "GRANTED" + consentTextId: "pp-sha256-a1b2c3d4..." + CREATE_CONSENT_REQUEST_DENIED: + summary: Create Consent request with status DENIED + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "DENIED" + consentTextId: "pp-sha256-a1b2c3d4..." + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateConsentResponseBody" + examples: + CREATE_CONSENT_RESPONSE: + summary: Create Consent response + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + CREATE_CONSENT_RESPONSE_EXPIRATION_DATE: + summary: Create Consent response with expiration date + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + "400": + $ref: "#/components/responses/Consent400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Consent403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + /consents/{consentId}: + patch: + summary: Update User Consent + description: | + This operation allows the API Consumer to update the status of an existing Consent for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The expiration date of the User Consent updated by the API Consumer will be determined by the API Provider's internal policies. The API Consumer cannot set or modify the expiration date of the User Consents captured in a delegated manner. + operationId: updateConsent + security: + - openId: + - consent-management:update + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: consentId + in: path + required: true + description: The unique identifier of the User Consent + schema: + type: string + example: "consent-123456" + requestBody: + required: true + description: updateConsent operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/UpdateConsentRequestBody" + examples: + UPDATE_CONSENT_REQUEST_DENIED: + summary: Update Consent status to DENIED + value: + consentStatus: "DENIED" + UPDATE_CONSENT_REQUEST_GRANTED: + summary: Update Consent status to GRANTED + value: + consentStatus: "GRANTED" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/UpdateConsentResponseBody" + examples: + UPDATE_CONSENT_RESPONSE: + summary: Update Consent response + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + UPDATE_CONSENT_RESPONSE_EXPIRATION_DATE: + summary: Update Consent response with expiration date + value: + consentId: "consent-123456" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + /consents/retrieve-info: + post: + summary: Retrieve Consent Information + description: | + This operation allows the API Consumer to retrieve information about the Consent(s) for a given User, scope(s) and Purpose. The API Consumer is identified by the `client_id` parameter deduced from the access token. + + The API Consumer can request that the texts intended for or previously shown to the User during the Consent Capture process for the requested scope(s) and Purpose be included in the response. If so, the `consentText` field will be included in the response for each matching Consent Information entry. + + The operation response may require more than one array item for the requested scope(s) and Purpose. For example, this may occur when the requested scopes relate to multiple APIs with independent User Consents. + + If the combination of the specified scope(s) and Purpose is permitted for the API Consumer but does not match any API(s) under Consent legal basis, an empty array will be returned. + operationId: retrieveConsentInfo + security: + - openId: + - consent-management:retrieve-info + tags: + - Consent Management + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/Accept-Language" + requestBody: + required: true + description: retrieveConsentInfo operation request body + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveConsentInfoRequestBody" + examples: + RETRIEVE_CONSENT_INFO_REQUEST: + summary: Retrieve Consent Information request + value: + phoneNumber: "+123456789" + scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + requestConsentText: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Language: + $ref: "#/components/headers/Content-Language" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveConsentInfoResponseBody" + examples: + RETRIEVE_CONSENT_INFO_PENDING: + summary: Retrieve Consent Information PENDING + description: Retrieve Consent Information when the User Consent is in PENDING status + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentStatus: "PENDING" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_REQUESTED: + summary: Retrieve Consent Information REQUESTED + description: Retrieve Consent Information when the User Consent is in REQUESTED status + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "REQUESTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_DENIED: + summary: Retrieve Consent Information DENIED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "DENIED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_GRANTED: + summary: Retrieve Consent Information GRANTED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "GRANTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_EXPIRED: + summary: Retrieve Consent Information EXPIRED + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "EXPIRED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2025-10-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + RETRIEVE_CONSENT_INFO_MULTIPLE_APIS: + summary: Retrieve Consent Information for multiple APIs + description: Retrieve Consent Information when the requested scopes relate to multiple APIs + value: + - scopes: + - "location-verification:verify" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-123456" + consentStatus: "GRANTED" + creationDate: "2025-07-03T14:27:08.312+02:00" + expirationDate: "2026-07-03T14:27:08.312+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: "pp-sha256-a1b2c3d4..." + lastUpdate: "2025-07-03T14:27:08.312+02:00" + - scopes: + - "device-roaming-status:read" + purpose: "dpv:FraudPreventionAndDetection" + consentId: "consent-654321" + consentStatus: "DENIED" + creationDate: "2025-08-15T10:00:00.000+02:00" + expirationDate: "2026-08-15T10:00:00.000+02:00" + consentText: + title: "Consent Required" + description: "Please provide your consent to proceed with roaming verification for fraud prevention." + consentTextId: "pp-sha256-e5f6g7h8..." + lastUpdate: "2025-08-15T10:00:00.000+02:00" + RETRIEVE_CONSENT_INFO_EMPTY_ARRAY: + summary: Retrieve Consent Information with no matching API(s) under Consent legal basis + description: Retrieve Consent Information when there are no matching API(s) under Consent legal basis for the specified scope(s) and Purpose + value: [] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Consent403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Language: + description: | + The language of the response content, following the standard defined in [RFC 7231, Section 5.3.5](https://datatracker.ietf.org/doc/html/rfc7231#section-5.3.5) using language tags as defined by [BCP 47](https://tools.ietf.org/html/bcp47). + + This header may be included in the response to indicate the language used for the response content when the API Consumer supplies an `Accept-Language` request header. If supported, the API Provider should select the preferred language indicated in the `Accept-Language` header. If the `Accept-Language` header is not present in the request, this header may instead be included to specify the API Provider’s default response language. + schema: + $ref: "#/components/schemas/LanguageTags" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Accept-Language: + name: Accept-Language + in: header + description: | + The preferred language for the response content. It follows the standard defined in [RFC 7231, Section 5.3.5](https://datatracker.ietf.org/doc/html/rfc7231#section-5.3.5) using language tags as defined by [BCP 47](https://tools.ietf.org/html/bcp47). + + The `Accept-Language` header field can be used by API Consumers to indicate the set of natural languages that are preferred in the response. If not provided, it implies that the API Consumer will accept any language in response and the API Provider will use its default language for the response content. + schema: + $ref: "#/components/schemas/LanguageTags" + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + CreateConsentRequestBody: + type: object + description: | + The request body for the createConsent operation. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - consentStatus + - consentTextId + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + consentStatus: + $ref: "#/components/schemas/CreateConsentStatus" + consentTextId: + $ref: "#/components/schemas/ConsentTextId" + Scopes: + type: array + minItems: 1 + items: + type: string + description: | + List of requested scopes. The scope is a string that represents the access rights that the API Consumer is requesting from the User. + example: + - "location-verification:verify" + Purpose: + type: string + pattern: '^dpv:[a-zA-Z0-9]+$' + description: | + The reason for which personal data will be processed by the API Consumer. CAMARA defines a standard set of Purposes which can be used by API Consumers to specify the reason for their intended personal data processing. CAMARA uses the [W3C Data Privacy Vocabulary](https://w3c.github.io/dpv/2.0/dpv/) (DPV) to represent these purposes e.g. `dpv:FraudPreventionAndDetection` or `dpv:RequestedServiceProvision`. + example: "dpv:FraudPreventionAndDetection" + CreateConsentStatus: + type: string + description: | + The status of the User Consent being created. It must represent the final outcome resulting from the Consent Capture process with the User. The only allowed values are `GRANTED` and `DENIED` when creating a Consent. + + - `GRANTED`: The User has given their Consent to allow the requested data processing. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + enum: + - GRANTED + - DENIED + example: "GRANTED" + CreateConsentResponseBody: + type: object + description: The response body for the createConsent operation + required: + - consentId + - creationDate + properties: + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + UpdateConsentRequestBody: + type: object + description: | + The request body for the updateConsent operation. It allows updating the status of an existing User Consent. + properties: + consentStatus: + $ref: "#/components/schemas/UpdateConsentStatus" + UpdateConsentStatus: + type: string + description: | + The status of the User Consent being updated. The only allowed values are `GRANTED` and `DENIED` when updating a Consent. + + - `GRANTED`: The User has given their Consent to allow the requested data processing e.g. after previously denying it or when renewing an expired Consent. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + enum: + - GRANTED + - DENIED + example: "DENIED" + UpdateConsentResponseBody: + type: object + description: The response body for the updateConsent operation + required: + - consentId + - creationDate + properties: + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + RetrieveConsentInfoRequestBody: + type: object + description: | + The request body for the retrieveConsentInfo operation. It contains the requested scope(s), the Purpose for which the API Consumer intends to process the User's personal data and optionally the phone number of the User. The phone number is required when the API is invoked using a two-legged access token, but MUST NOT be provided when a three-legged access token is used, as the subject will be uniquely identified from the access token. + required: + - scopes + - purpose + - requestConsentText + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + requestConsentText: + type: boolean + description: | + Indicates whether the texts intended for or previously shown to the User during the Consent Capture process for the requested scope(s) and Purpose should be included in the response. + + If set to `true`, the `consentText` field will be included in the response for each matching Consent Information entry. If set to `false`, the `consentText` field will be omitted from the response. + example: true + RetrieveConsentInfoResponseBody: + type: array + description: The response body for the retrieveConsentInfo operation + items: + $ref: "#/components/schemas/ConsentInfoItem" + ConsentInfoItem: + type: object + required: + - scopes + - purpose + - consentStatus + properties: + scopes: + $ref: "#/components/schemas/Scopes" + purpose: + $ref: "#/components/schemas/Purpose" + consentId: + type: string + description: The unique identifier of the User Consent + example: "consent-123456" + consentStatus: + $ref: "#/components/schemas/ConsentStatus" + consentText: + $ref: "#/components/schemas/ConsentText" + creationDate: + $ref: "#/components/schemas/CreationDate" + expirationDate: + $ref: "#/components/schemas/ExpirationDate" + ConsentStatus: + type: string + description: | + The status of the User Consent. The allowed values are: + + - `PENDING`: The User Consent is pending and has not yet been requested from the User. + - `REQUESTED`: The User Consent has been requested from the User, but the User has not yet responded. + - `GRANTED`: The User has given their Consent to allow the requested data processing. + - `DENIED`: The User has refused to give their Consent for the requested data processing. + - `EXPIRED`: The User Consent has expired and is no longer valid. + enum: + - PENDING + - REQUESTED + - GRANTED + - DENIED + - EXPIRED + example: "GRANTED" + ConsentText: + type: object + description: | + The texts presented to the User during the Consent Capture process for the requested scope(s) and Purpose. + + It is composed of a title and a description, both of which are localized texts provided in the language indicated by the `Content-Language` response header (if present). There is also a unique, immutable string identifier, called a `consentTextId`, that designates a specific, versioned instance of a legal text. An optional `lastUpdate` timestamp can be included to indicate when the consent text version was last updated by the API Provider. + + These texts are only included in the response when explicitly requested by setting the `requestConsentText` field to `true` in the request. + required: + - title + - description + - consentTextId + properties: + title: + type: string + description: The localized text title + example: "Consent Required" + description: + type: string + description: The localized text description + example: "Please provide your consent to proceed with location verification for fraud prevention." + consentTextId: + $ref: "#/components/schemas/ConsentTextId" + lastUpdate: + type: string + format: date-time + description: | + The date and time when this consent text version was last updated. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2025-07-03T14:27:08.312+02:00" + LanguageTags: + type: string + description: List of Language tags that identify natural languages, following [BCP 47](https://tools.ietf.org/html/bcp47) standard. + example: "en-US" + ConsentTextId: + type: string + description: | + This is a unique, immutable (e.g. hash-based) string identifier that designates a specific version of a legal text presented to the User during the Consent Capture process. + + The API consumer MUST submit this exact, unaltered identifier when creating a User Consent. + + This identifier creates a traceable, auditable link that binds a User's Consent to the specific textual content they were shown. + example: "pp-sha256-a1b2c3d4..." + CreationDate: + type: string + format: date-time + description: | + The date and time at which the User Consent was created. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2025-07-03T14:27:08.312+02:00" + ExpirationDate: + type: string + format: date-time + description: | + The date and time at which the validity of the User Consent is set to expire or has expired (when applicable). The API Provider determines the expiration date based on its internal policies. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + example: "2026-07-03T14:27:08.312+02:00" + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Consent400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - CONSENT_MGMT.INVALID_CONSENT_TEXT_ID + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + INVALID_CONSENT_TEXT_ID: + description: The provided consentTextId does not match any valid consent text version available for the requested scope(s) and Purpose. + value: + status: 400 + code: CONSENT_MGMT.INVALID_CONSENT_TEXT_ID + message: The consentTextId provided is either invalid or does not exist. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Consent403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - CONSENT_MGMT.NOT_ALLOWED_SCOPES_PURPOSE + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + NOT_ALLOWED_SCOPES_PURPOSE: + description: The requested scope(s) and Purpose combination is not allowed for the API Consumer, e.g. the API Consumer has not onboarded the appropriate API(s) with the API Provider for the declared Purpose. + value: + status: 403 + code: CONSENT_MGMT.NOT_ALLOWED_SCOPES_PURPOSE + message: The requested scope(s) and Purpose combination is not allowed for this API Consumer. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration diff --git a/original/ConsentManagement/documentation/API_documentation/README.MD b/original/ConsentManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConsentManagement/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ConsentManagement/documentation/SupportingDocuments/README.MD b/original/ConsentManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ConsentManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/CustomerInsights/README.md b/original/CustomerInsights/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8f43a6038a268e5f947ecad289b800fa75cc543c --- /dev/null +++ b/original/CustomerInsights/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# CustomerInsights + +Sandbox API Repository to describe, develop, document, and test the CustomerInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/owBuAQ) + +## Scope + +* Service APIs for “CustomerInsights” +* The API provides the customer with the ability to: + * Provides a risk index (a.k.a. Scoring) based on the individual's profile owned by a Telco Operator. + * So far two scoring scales are defined within the current proposal (GaugeMetric, VeritasIndex). +* Describe, develop, document, and test the APIs +* Started: October 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/CustomerInsights/releases/tag/r2.2) (Fall25), with the following API versions: + * **customer-insights v0.2.0** + [[YAML]](https://github.com/camaraproject/CustomerInsights/blob/r2.2/code/API_definitions/customer-insights.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/CustomerInsights/r2.2/code/API_definitions/customer-insights.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/CustomerInsights/r2.2/code/API_definitions/customer-insights.yaml) +* The latest public release is always available here: https://github.com/camaraproject/CustomerInsights/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/CustomerInsights/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/CustomerInsights/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly on Thursdays at 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95737002367?password=034d9b74-a944-4def-ae30-0f93802430a5) + * Minutes: Access [[meeting minutes]](https://lf-camaraproject.atlassian.net/wiki/x/XIBuAQ) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/CustomerInsights/code/API_definitions/customer-insights.yaml b/original/CustomerInsights/code/API_definitions/customer-insights.yaml new file mode 100644 index 0000000000000000000000000000000000000000..8cb78c294caafec1e61d73eef98485e72e77064b --- /dev/null +++ b/original/CustomerInsights/code/API_definitions/customer-insights.yaml @@ -0,0 +1,504 @@ +openapi: 3.0.3 +info: + description: |- + Allows the API consumer to retrieve a risk index based on the individual's profile owned by a Telco Operator. + + # Relevant Definitions and concepts + + * **Scoring**: risk classification based on the individual's profile owned by a Telco Operator, i.e.: a rating on a scale that represents the risk index based on financial, socioeconomic and consumption data. + + Two different scales are considered for the Scoring: + + * **GaugeMetric**: Scoring scale that ranges from index 850 (lowest risk) to index 300 (highest risk), thus the higher the value of the index, the lower the risk it represents. This numerical scale is based on the globally recognized FICO score system. Values meaning is as follows: + + 800-850: Exceptional, very low risk. + + 740-799: Very Good, low risk. + + 670-739: Good, moderate risk. + + 580-669: Fair, higher risk. + + 300-579: Poor, very high risk. + + + * **VeritasIndex**: Scoring scale that ranges from index 0 (lowest risk) to index 19 (highest risk), thus the lower the value of the index, the lower the risk it represents. This numerical scale can be related with _alphabetical_ identifiers similar to those used by major rating agencies such as Standard & Poor's, Moody's and Fitch. Values meaning is as follows: + + 0-1 AAA + 2-3 AA + 4-5 A + 6-7 BBB + 8-9 BB + 10-11 B + 12-13 CCC + 14-15 CC + 16-17 C + 18-19 DDD + + # API Functionality + + This API allows to retrieve the Scoring information of a user within the operator. + + # Resources and Operations overview + + The API provides the following endpoint: + + - An operation to retrieve Scoring information. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + title: Customer Insights + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: wip +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/CustomerInsights +servers: + - url: "{apiRoot}/customer-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider +tags: + - name: Scoring + description: Operations to retrieve Scoring information. +paths: + /scoring/retrieve: + post: + security: + - openId: + - customer-insights:scoring:read + tags: + - Scoring + summary: Retrieves Scoring information + description: >- + Retrieves Scoring information, for the user associated with the provided `idDocument`, `phoneNumber` or the combination of both parameters. + + It also allows to select the type of the Scoring scale measurement. + operationId: retrieveScoring + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/ScoringRequest" + examples: + INPUT_GAUGE_METRIC: + summary: Gauge Metric + description: Gauge Metric score request, with no additional information. Default three-legged access mode for Gauge Metric + value: + scoringType: gaugeMetric + INPUT_VERITAS_INDEX: + summary: Veritas Index + description: Veritas Index score request, with no additional information. Default three-legged access mode for Veritas index + value: + scoringType: veritasIndex + INPUT_GAUGE_METRIC_PHONENUMBER: + summary: Gauge Metric with phoneNumber + description: Gauge Metric score request, with phoneNumber. Default two-legged access mode for Gauge Metric + value: + phoneNumber: "+556253423432" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_PHONENUMBER: + summary: Veritas Index with phoneNumber + description: Veritas Index score request, with phoneNumber. Default two-legged access mode for Veritas index + value: + phoneNumber: "+556253423432" + scoringType: veritasIndex + INPUT_GAUGE_METRIC_ID_DOCUMENT: + summary: Gauge Metric with idDocument + description: Gauge Metric score request, with idDocument. + value: + idDocument: "987654321" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_ID_DOCUMENT: + summary: Veritas Index with idDocument + description: Veritas Index score request, with idDocument. + value: + idDocument: "987654321" + scoringType: veritasIndex + INPUT_GAUGE_METRIC_PHONENUMBER_ID_DOCUMENT: + summary: Gauge Metric with phoneNumber and idDocument + description: Gauge Metric score request, with phoneNumber and idDocument. + value: + idDocument: "987654321" + phoneNumber: "+556253423432" + scoringType: gaugeMetric + INPUT_VERITAS_INDEX_PHONENUMBER_ID_DOCUMENT: + summary: Veritas Index with phoneNumber and idDocument + description: Veritas Index score request, with phoneNumber and idDocument. + value: + idDocument: "987654321" + phoneNumber: "+556253423432" + scoringType: veritasIndex + responses: + "200": + description: Scoring result. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ScoringResponse" + examples: + GAUGE_METRIC: + summary: Gauge Metric Response + description: Scoring with Gauge Metric index + value: + scoringType: gaugeMetric + scoringValue: 600 + VERITAS_INDEX: + summary: Veritas Index Response + description: Scoring with Veritas Index + value: + scoringType: veritasIndex + scoringValue: 4 + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + ScoringRequest: + type: object + properties: + idDocument: + type: string + description: |- + Identification number associated to the official identity document in the country. It may contain alphanumeric characters. + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + scoringType: + type: string + description: |- + Scoring type, i.e.: scale. API Client may use this field to indicate the Scoring in one of the defined scales; if this field is not informed, the API will return the Scoring in the scale configured by default in the system. + + Allowed values are: + + * `gaugeMetric`: ranges from index 850 (lowest risk) to index 300 (highest risk) + * `veritasIndex`: ranges from index 0 (lowest risk) to index 19 (highest risk) + enum: + - gaugeMetric + - veritasIndex + ScoringResponse: + type: object + description: Scoring information based on the individual's profile owned by a Telco Operator. + required: + - scoringType + - scoringValue + properties: + scoringType: + type: string + description: |- + Scoring measurement system. + + Allowed values are: + + * `gaugeMetric`: ranges from index 850 (lowest risk) to index 300 (highest risk) + * `veritasIndex`: ranges from index 0 (lowest risk) to index 19 (highest risk) + enum: + - gaugeMetric + - veritasIndex + scoringValue: + type: integer + description: Result of the Scoring analysis expressed in the measure indicated in the `scoringType` field. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: |- + Problem with the client request. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + InvalidArgument: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: |- + Not found + + In addition to regular NOT_FOUND scenario, another scenarios may exist: + - Phone Number not found ("code": "IDENTIFIER_NOT_FOUND","message": "phoneNumber not found."). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device. In this API it refers to a phoneNumber. + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: phoneNumber not found. + Generic422: + description: |- + Unprocessable Content + + In addition to regular scenario of Unprocessable Content, another scenarios may exist. + - Service not applicable for the provided identifier ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided identifier.") + - An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The phone number cannot be identified.") + - An explicit identifier is provided when a device or phone number has already been identified from the access token ("code": "UNNECESSARY_IDENTIFIER","message": "The phone number is already identified by the access token.") + - Provided `scoringType` value is not supported. (`"code": "CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED","message": "Indicated parameter scoringType is not supported."`) + - Provided `idDocument` is not consistent with the phone number. (`"code": "CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS","message": "The request contains invalid data."`) + - Provided `idDocument` field is not supported. (`"code": "CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED","message": "Indicated parameter idDocument is not supported"`) + - Required `idDocument` field and it is not provided. (`"code": "CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED","message": "The idDocument is required to perform the properties validation."`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED + - CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS + - CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED + - CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token. + GENERIC_422_NOT_SUPPORTED_SCORING_TYPE_VALUE: + description: Error when `scoringType` value is not supported. + value: + status: 422 + code: CUSTOMER_INSIGHTS.SCALE_TYPE_NOT_SUPPORTED + message: Indicated parameter `scoringType` is not supported. + GENERIC_422_INVALID_IDENTIFIERS: + description: The request contains invalid data identifying customer + value: + status: 422 + code: CUSTOMER_INSIGHTS.INVALID_IDENTIFIERS + message: The request contains invalid data. + GENERIC_422_ID_DOCUMENT_NOT_SUPPORTED: + description: Error when `idDocument` field is not supported + value: + status: 422 + code: CUSTOMER_INSIGHTS.ID_DOCUMENT_NOT_SUPPORTED + message: Indicated parameter `idDocument` is not supported + GENERIC_422_ID_DOCUMENT_REQUIRED: + description: Error when `idDocument` field is not provided and it is required. + value: + status: 422 + code: CUSTOMER_INSIGHTS.ID_DOCUMENT_REQUIRED + message: The `idDocument` is required to perform the properties validation. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - TOO_MANY_REQUESTS + examples: + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist.md b/original/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..e789470bbab4c5fa683641ef7dad013d7db0eff0 --- /dev/null +++ b/original/CustomerInsights/documentation/API_documentation/customer-insights-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Customer Insights v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference Information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/customer-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [link](/code/API_definitions/customer-insights.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/customer-insights-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | link | +| 9 | Test result statement | O | O | O | M | N | link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/RYHWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/CustomerInsights/documentation/API_documentation/customer-insights-User-Story.md b/original/CustomerInsights/documentation/API_documentation/customer-insights-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..1030fcde77363c634fff6aa846c572f836cc244f --- /dev/null +++ b/original/CustomerInsights/documentation/API_documentation/customer-insights-User-Story.md @@ -0,0 +1,24 @@ +**User Story: Credit scoring service for banking** +
                                                          + +| **Item** | **Details** | +| -------- | ----------- | +| ***Summary*** | As a bank officer, I want to evaluate a micro-credit application for a customer who has no credit history within our bank. I use the Customer Insights API to gather additional information about the customer's telco behavior to assess their creditworthiness. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                          **Actors:** Bank Officer, Bank System, Communication Service Provider (CSP)
                                                          **Scope:** Retrieve a relevant score calculated from the data of the CSP, enabling the bank to make an informed decision on micro-credit approval. | +| ***Pre-conditions*** | The preconditions are listed below:
                                                          1. The bank is integrated with the CSP's Customer Insights API.
                                                          2. The customer has consented (3-legged scenarios) to sharing their telco data for credit assessment purposes.
                                                          3. The bank officer has the necessary credentials to access the Customer Insights API.
                                                          | +| ***Activities/Steps*** | **Begins when:** The bank officer submits a micro-credit application for a customer without an existing credit history.

                                                          **Steps include:**
                                                          1. The bank system makes a request to the Customer Insights API using customer consented information.
                                                          2. The CSP processes the request and gathers telco-related behavioral insights.
                                                          3. The CSP sends a calculated score to the bank system.
                                                          4. The bank officer evaluates the score to assess the credit risk of the customer.

                                                          **Ends when:** The bank officer either approves or declines the micro-credit application based on the insights provided. | +| ***Post-conditions*** | The bank officer has sufficient data to approve or deny the micro-credit request for a customer without a traditional credit history. | +| ***Exceptions*** | Several exceptions might occur during the Customer Insights API operations:
                                                          - Unauthorized: Invalid credentials provided by the bank system.
                                                          - Consent missing: The customer has not provided consent for sharing telco data (i.e. permission denied).
                                                          - Data not found: Insufficient user data available for the customer.
                                                          - Corporate customers: The API is not applicable for corporate customers. | + + +**User Story: Credit scoring service for riders** +
                                                          + +| **Item** | **Details** | +| -------- | ----------- | +| ***Summary*** | As a service provider, I want to evaluate the creditworthiness of riders working for food delivery, errands, and other similar applications. I use the Customer Insights API to generate a score for these riders, which can be used by companies and banks to offer credit services to the riders for purchasing a motorcycle, bicycle, or electric scooter. The application can leverage the Customer Insights API to complement the score generated with additional telco data, enhancing the overall credit score. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                          **Actors:** Service Provider, Bank System, Rider, Application Service Provider (ASP), Communication Service Provider (CSP)
                                                          **Scope:** Retrieve relevant behavioral data about the riders from both the delivery apps and the CSP, enabling a comprehensive credit score calculation to support credit decisions for vehicle purchases. | +| ***Pre-conditions*** | The preconditions are listed below:
                                                          1. The service provider is integrated with both the delivery applications and the CSP's Customer Insights API.
                                                          2. The rider has consented (3-legged scenarios) to share their delivery and telco data for credit assessment purposes.
                                                          3. The service provider has the necessary credentials to access Customer Insights API and the path to route to the right CSP.
                                                          | +| ***Activities/Steps*** | **Begins when:** The service provider initiates a credit assessment for a rider interested in purchasing a vehicle (motorcycle, bicycle, or electric scooter).

                                                          **Steps include:**
                                                          1. The service provider collects rider activity data from the delivery applications, including job completion rates, earnings, and overall performance.
                                                          2. Optionally and out of the scope of CAMARA API, The service provider can make a request to other External Platforms API(s) available in the market (solution outside CAMARA, but to illustrate a real use case) using the collected data and rider consent details.
                                                          3. The external ASP processes the request and generates a preliminary credit score based on the rider's delivery activities.
                                                          4. The service provider then makes a request to the Customer Insights API to retrieve additional telco-related score about the rider.
                                                          5. The CSP processes the request and gathers telco-related behavioral insights. The CSP sends a final enhanced credit score to the service provider.
                                                          6. The service provider evaluates the received scores to assess the rider's creditworthiness for purchasing a vehicle.

                                                          **Ends when:** The service provider either approves or declines the credit application based on the insights provided. | +| ***Post-conditions*** | The service provider has sufficient data to approve or deny the credit request for a rider based on a comprehensive score derived from both delivery app activity and telco data. | +| ***Exceptions*** | Several exceptions might occur during the Customer Insights API operations:
                                                          - Unauthorized: Invalid credentials provided by the service provider.
                                                          - Consent missing: The rider has not provided consent for sharing delivery or telco data (i.e. permission denied).
                                                          - Data not found: Insufficient data available from delivery apps or telco records for the rider.
                                                          - Corporate customers: The API is not applicable for corporate customers. | diff --git a/original/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition.md b/original/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition.md new file mode 100644 index 0000000000000000000000000000000000000000..a5a38090c97f4cc768800eb609e34b3f850178b6 --- /dev/null +++ b/original/CustomerInsights/documentation/API_documentation/customer-insights-algorithm-model-definition.md @@ -0,0 +1,107 @@ +# Algorithm Model Definition + +This document reflects the CAMARA WG Recommendation regarding the concepts to be evaluated for the implementation of the underlying algorithm for a specific scoring model. + +CAMARA WG recognizes this is a non-exhaustive list: +* This list can be enhanced from the learning and experience gained across different implementations +* An algorithm implementation is not required to support all the concepts listed below. Such a decision will be market by market case (i.e. country, by means of a consensus among Operators involved) + +The list of concepts is depicted below: + +| **ORDER (NOTE 1)** | **CONCEPT/PARAMETER (NOTE 2)** | **DESCRIPTION** | **FORMAT (NOTE 3)** | **ADDITIONAL COMMENTS** | **BASELINE CONCEPT (NOTE 4)**| +|:-------------------|:------------------------------:|:----------------|:-------------------:|:------------------------|:-----------------------------| +| #1 | subscription_type | Contract type (Postpay, Prepay, Control/Hybrid) | string | N/A | YES | +| #2 | customer_since_months | Time since the customer belongs to the Telco Operator in months | integer | N/A | YES | +| #3 | outgoing_calls_minutes_in_{period} | Accumulated time of outgoing calls in minutes in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #4 | outgoing_sms_in_{period} | Accumulated number of outgoing sms in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #5 | outgoing_data_{unit}_{subscription}\_in\_{period} | Accumulated outgoing data session in agreed {units}, {subscription} and {period} in the specific market:
                                                          * {units}: MB or GB
                                                          * {subscription}: Postpay, Prepay or Control/Hybrid (mixed case of Postpay/Prepay)
                                                          * {period}: 1 month, 3 months, 6 months, ... | decimal | N/A | YES | +| #6 | incoming_calls_minutes_in_{period} | Accumulated time of incoming calls in minutes in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #7 | incoming_sms_in_{period} | Accumulated number of incoming sms in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES | +| #8 | arpu_in_{period} | Average revenue per user (ARPU), sometimes known as average revenue per unit, is a measure used primarily by consumer communications, digital media, and networking companies, defined as the total revenue divided by the number of subscribers in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | YES +| #9 | average_billing_amount_in_{period} | Average Billing Amount in the official market currency in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #10 | average_recharge_amount_in_{period} | Average Recharge Amount in the official market currency in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #11 | max_payment_due_date_delay_in_{period} | Maximum number of days the customer delayed his payment (after due date) in the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...). Only applies to Postpay or Control/Hybrid | integer | N/A | NO | +| #12 | max_overdue_balance_in_{period} | Maximum balance amount in the official market currency that was not paid by due date over the last {period} agreed in the specific market (1 month, 3 months, 6 months, ...) | decimal | N/A | NO | +| #13 | geographical_numbering_area | Geographical Numbering Area, representing the part of the phone number that is linked to a geographical (Fixed or Mobile Area). | integer | Used for instance in payments, when Telco Operator has the historical payments of customers and their ubication, in order to check number of payments and their amount (i.e. to check whether he/she is a good payer). | NO | +| #14 | social_net_data_{unit}_{subscription}\_in\_{period} | Accumulated outgoing data session consumed in Social Networks in agreed {units}, {subscription} and {period} in the specific market:
                                                          * {units}: MB or GB
                                                          * {subscription}: Postpay, Prepay or Control/Hybrid (mixed case of Postpay/Prepay)
                                                          * {period}: 1 month, 3 months, 6 months, ... | decimal | This concept may have GDPR constraints in a given market to be considered. Please check regulation in the market/country for the consideration of this concept. | NO | + + +**NOTE 1**: This is a recommenadation for consideration order in the algorithm.
                                                          +**NOTE 2**: This is an informative name, the exact name of the parameter is up to the implementation.
                                                          +**NOTE 3**: This is a recommendation. Up to the implementation agreed in a specific market.
                                                          +**NOTE 4**: This is a recommendation about which concepts (marked with YES) could be considered as potential baseline for initial implementations. The others (marked with NO) would be considered as advanced features.
                                                          + +Below table shows the Telco Operator source system that hosts the above concepts: + +| **CONCEPT/PARAMETER** | **TELCO OPERATOR SOURCE SYSTEM** | +|:---------------------:|:---------------------------------| +| subscription_type | BSS | +| customer_since_months | BSS. Also related to [Tenure API functionality](https://github.com/camaraproject/Tenure) | +| outgoing_calls_minutes_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| outgoing_sms_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| outgoing_data_{unit}_{subscription}\_in\_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| incoming_calls_minutes_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| incoming_sms_in_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | +| arpu_in_{period} | BSS and CRM | +| average_billing_amount_in_{period} | OFCS and Billing System | +| average_recharge_amount_in_{period} | OCS | +| max_payment_due_date_delay_in_{period} | Billing System | +| max_overdue_balance_in_{period} | Billing System | +| geographical_numbering_area | HLR/HSS (Geographical Numbering Area may be part of the phoneNumber in some countries, e.g. Brazil Numbering +55**11**xxxxxxxx) | +| social_net_data_{unit}_{subscription}\_in\_{period} | OCS for prepay // OFCS for postpay // Both for control/hybrid | + +LEGEND: +- BSS: Business Support Systems +- CRM: Customer Relationship Management +- HLR: Home Location Register +- HSS: Home Subscriber Server +- OCS: Online Charging System +- OFCS: Offline Charging System + + +## INFORMATIVE: Algorithm Model implementation examplification + +This section provides an example about how to the algorithm could be implemented. +The specific implementation approach in a given market MUST be discussed and agreed among involved participants (i.e. Telco Operators) in such a market. + +Below example considers: +- `veritasIndex` scoring +- postpay and prepay subscriptions in market +- period of 1 month +- data units in GB +- Indicated weight for each concept considered +- Concepts considered: The ones tagged as Baseline concepts (first eight ones) +- Example ranges for each concept associated to each score range + + +| **CONCEPT/PARAMETER** | **WEIGHT(%)** | **SCORE 0** | **SCORE 1** | **SCORE 2** | **SCORE 3** | **SCORE 4** | **SCORE 5** | **SCORE 6** | **SCORE 7** | **SCORE 8** | **SCORE 9** | **SCORE 10** | **SCORE 11** | **SCORE 12** |**SCORE 13** | **SCORE 14** | **SCORE 15** | **SCORE 16** | **SCORE 17** | **SCORE 18** | **SCORE 19** | +|:---------------------:|:----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:-----------:|:------------:|:------------:|:------------:|:-----------:|:------------:|:------------:|:------------:|:------------:|:------------:|:------------:| +| subscription_type | 12,5 | N/A | N/A | N/A | N/A | postpay | N/A | N/A | N/A | N/A | N/A | N/A | N/A | N/A | N/A | prepay | N/A | N/A | N/A | N/A | N/A | +| customer_since_months | 12,5 | x > 120 | 96 < x <= 120 | 72 < x <= 96 | 60 < x <= 72 | 48 < x <= 60 | 36 < x <= 48 | 24 < x <= 36 | 12 < x <= 24 | 11 < x <= 12 | 10 < x <= 11 | 9 < x <= 10 | 8 < x <= 9 | 7 < x <= 8 | 6 < x <= 7 | 5 < x <= 6 | 4 < x <= 5 | 3 < x <= 4 | 2 < x <= 3 | 1 < x <= 2 | 0 <= x <= 1 | +| outgoing_calls_minutes_in_{period} | 12,5 | x > 1140 | 1080 < x <= 1140 | 1020 < x <= 1080 | 960 < x <= 1020 | 900 < x <= 960 | 840 < x <= 900 | 780 < x <= 840 | 720 < x <= 780 | 660 < x <= 720 | 600 < x <= 660 | 540 < x <= 600 | 480 < x <= 540 | 420 < x <= 480 | 360 < x <= 420 | 300 < x <= 360 | 240 < x <= 300 | 180 < x <= 240 | 120 < x <= 180 | 60 < x <= 120 | 0 <= x <= 60 | +| outgoing_sms_in_{period} | 12,5 | > 100 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 35 < x <= 40 | 30 < x <= 35 | 25 < x <= 30 | 20 < x <= 25 | 17 < x <= 20 | 14 < x <= 17 | 12 < x <= 14 | 10 < x <= 12 | 8 < x <= 10 | 6 < x <= 8 | 4 < x <= 6 | 2 < x <= 4 | 0 <= x <= 2 | +| outgoing_data_{unit}_{subscription}\_in\_{period} | 12,5 | x > 160 | 150 < x <= 160 | 140 < x <= 150 | 130 < x <= 140 | 120 < x <= 130 | 110 < x <= 120 | 100 < x <= 110 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 30 < x <= 40 | 25 < x <= 30 | 20 < x <= 25 | 15 < x <= 20 | 10 < x <= 15 | 5 < x <= 10 | 0 <= x <= 5 | +| incoming_calls_minutes_in_{period} | 6,25 | x > 570 | 540 < x <= 570 | 510 < x <= 540 | 480 < x <= 510 | 450 < x <= 480 | 420 < x <= 450 | 390 < x <= 420 | 360 < x <= 390 | 330 < x <= 360 | 300 < x <= 330 | 270 < x <= 300 | 240 < x <= 270 | 210 < x <= 240 | 180 < x <= 210 | 150 < x <= 180 | 120 < x <= 150 | 90 < x <= 120 | 60 < x <= 90 | 30 < x <= 60 | 0 <= x <= 30 | +| incoming_sms_in_{period} | 6,25 | x > 57 | 54 < x <= 57 | 51 < x <= 54 | 48 < x <= 51 | 45 < x <= 48 | 42 < x <= 45 | 39 < x <= 42 | 36 < x <= 39 | 33 < x <= 36 | 30 < x <= 33 | 27 < x <= 30 | 24 < x <= 27 | 21 < x <= 24 | 18 < x <= 21 | 15 < x <= 18 | 12 < x <= 15 | 9 < x <= 12 | 6 < x <= 9 | 3 < x <= 6 | 0 <= x <= 3 | +| arpu_in_{period} | 25 | x > 190 | 180 < x <= 190 | 170 < x <= 180 | 160 < x <= 170 | 150 < x <= 160 | 140 < x <= 150 | 130 < x <= 140 | 120 < x <= 130 | 110 < x <= 120 | 100 < x <= 110 | 90 < x <= 100 | 80 < x <= 90 | 70 < x <= 80 | 60 < x <= 70 | 50 < x <= 60 | 40 < x <= 50 | 30 < x <= 40 | 20 < x <= 30 | 10 < x <= 20 | 0 <= x <= 10 | + + +**User A scenario score calculation** + +| **CONCEPT/PARAMETER** | **WEIGHT(%)** | **VALUE** | **MAPPED SCORE** | **WEIGHTED SCORE** | **SCORE** | +|:---------------------:|:-------------:|:---------:|:----------------:|:------------------:|:---------:| +| subscription_type | 12,5 | postpay | 4 | 0,5 | N/A | +| customer_since_months | 12,5 | 60 | 4 | 0,5 | N/A | +| outgoing_calls_minutes_in_{period} | 12,5 | 600 | 10 | 1,25 | N/A | +| outgoing_sms_in_{period} | 12,5 | 15 | 12 | 1,5 | N/A | +| outgoing_data_{unit}_{subscription}\_in\_{period} | 12,5 | 100 | 7 | 0,875 | N/A | +| incoming_calls_minutes_in_{period} | 6,25 | 300 | 10 | 0,625 | N/A | +| incoming_sms_in_{period} | 6,25 | 10 | 16 | 1 | N/A | +| arpu_in_{period} | 25 | 100 | 10 | 2,5 | N/A | +| scoringValue | 100% | N/A | N/A | 8,75 | 9 | + + +**scoringValue weighted score** is indicated in **column WEIGHTED SCORE** as the sum of the **WEIGHTED SCORE** of every concept.
                                                          +**scoringValue** is indicated in **column SCORE** rounding to the nearest integer of the **scoringValue weighted score** + +NOTE: This example uses `,` as the decimal separator as per the `ISO 80000-1` standard. diff --git a/original/CustomerInsights/documentation/SupportingDocuments/README.MD b/original/CustomerInsights/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/CustomerInsights/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DedicatedNetworks/README.md b/original/DedicatedNetworks/README.md new file mode 100644 index 0000000000000000000000000000000000000000..0d8108c3dd14ba6cc35260fc1a6fadb62ad0b044 --- /dev/null +++ b/original/DedicatedNetworks/README.md @@ -0,0 +1,69 @@ + + + + + + + + + +# DedicatedNetworks + +Sandbox API Repository to describe, develop, document, and test the DedicatedNetworks Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/hAClB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XIArAQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/OICGAQ) + +For background on Dedicated Networks concepts and workflows, see the [General Description](documentation/API_documentation/DedicatedNetworks_GeneralDescription.md). + +## Scope + +* Service APIs for DedicatedNetworks (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API Consumer with the ability to: + * request/modify/delete a (logical) Dedicated Network for API consumers. + * A Dedicated Network offers + * specific connectivity performance (e.g. speed/ latency) + * during a specific time duration (e.g. one hour) and + * at specific locations (e.g. the area of a festival) + * A Dedicated Network may be ensured by an SLA. + * API consumers are able to manage access to this dedicated network for specific devices. +* Describe, develop, document, and test the APIs +* Started: October 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DedicatedNetworks/releases/tag/r1.2) (Fall25), with the following API versions: + * **dedicated-network-accesses v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network-accesses.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-accesses.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-accesses.yaml) + * **dedicated-network-profiles v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network-profiles.yaml) + * **dedicated-network v0.1.0** + [[YAML]](https://github.com/camaraproject/DedicatedNetworks/blob/r1.2/code/API_definitions/dedicated-network.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DedicatedNetworks/r1.2/code/API_definitions/dedicated-network.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DedicatedNetworks/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DedicatedNetworks/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DedicatedNetworks/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: bi-weekly, Mondays, 10 AM CET (09:00 UTC). For date/time of the next meeting, see previous meeting minutes + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94505909302?password=67b9a175-154f-4fe1-986d-0b825227a95b) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/S3hQ1AFG) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using sp-cqm@lists.camaraproject.org. diff --git a/original/DedicatedNetworks/code/API_definitions/dedicated-network-accesses.yaml b/original/DedicatedNetworks/code/API_definitions/dedicated-network-accesses.yaml new file mode 100644 index 0000000000000000000000000000000000000000..a9773f6b80bd73d200a49bd0f7054f1341637c6e --- /dev/null +++ b/original/DedicatedNetworks/code/API_definitions/dedicated-network-accesses.yaml @@ -0,0 +1,962 @@ +openapi: 3.0.3 +info: + title: Dedicated Network - Accesses + description: | + + This API allows for requesting network access for devices. A device is identified by the CAMARA _device object_, containing either an MSIDSN or a Network Access Identifier. For more information about the Dedicated Networks APIs, see the _GeneralDescription_ document in the Dedicated Networks [repository](https://github.com/camaraproject/DedicatedNetworks/). + + A Device Access represents the permission for a specific device to use a Dedicated Network's reserved connectivity resources. Only devices for which a Device Access resource has been created can use the connectivity resources allocated for that network. The usage of resources can be tailored to each device within the constraints of the applicable Network Profile. + + A device is identified by the CAMARA `device` object, where at least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. + + Notes: + 1. Support for using an IP address as device identifier is not recommended when the IP address may change. The API invoker may not be able to associate the accesses resource with the targeted device anymore.
                                                          Further, the device may be offline at time of Accesses API usage, thus, no IP address assigned. + 1. Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device`, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same `device` is identified by these two methods, as the server is unable to make this comparison. + - If the number of devices with access to the network is equal to or exceeds the 'maxNumberOfDevices', the API provider will provide a `429 QUOTA_EXCEEDED` error code. + + # Creating a device access + + A Device Access is created by performing a `POST` operation on the `/accesses` endpoint. + + The API Consumer provides the following information + + - the networkId to which access is being given + + - identifier of the device - either in `device` object or in the token (see "Identifying the device from the access token" above) + + - optionally, a default QoS Profile can be set for the device (see Network Profiles section in the dedicated-network-profiles API in the [Dedicated Networks repository](https://github.com/camaraproject/DedicatedNetworks/)). + + - optionally, a subset of QoS Profiles from this network can be provided to further restrict which QoS Profiles the device can access + + - Optionally, callback related information through sink and sinkCredential parameters to receive notifications about the lifecycle events of the device access. + + The API returns an accessId. The accessId is a unique identifier of the device access, which remains unchanged during its lifetime. The accessId is needed to query the status of the Device Access (GET /accesses/{accessId}) and to delete Access (DELETE accesses/{accessId}). + + Initially, the device access is in `REQUESTED` state. The device access is only usable when it is in `GRANTED` state. + + + ## Error handling: + + - If the dedicated network identified by the networkId is in an incompatible state when creating a device access, e.g. it is in the TERMINATED state, then the server will return an error with the `409 INCOMPATIBLE_STATE` error code. + + # Querying one or more device accesses + + All available device accesses of the API consumer can be queried by performing a `GET` operation on the `/accesses` endpoint. The query can be filted for accesses to a specific network (networkId) or for certain devices. + + A specific device access of the API consumer can be queried by performing a `GET` operation on the `/accesses/{accessId}` endpoint, where the accessId has been obtained during the _create_ procedure. + + # Deleting a device accesses + + A specific device access of the API consumer can be deleted by performing a `DELETE` operation on the `/accesses/{accessId}` endpoint. Deletion of the access can be interpreted as removal of the access permissions. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network-accesses/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Accesses + description: Manage accesses of devices for a dedicated network +paths: + + /accesses: + get: + tags: + - Accesses + summary: Get a list of device accesses to dedicated networks, optionally filtered for a given device and/or for a given dedicated network + operationId: listNetworkAccesses + security: + - openId: + - dedicated-network-accesses:accesses:read + parameters: + - name: networkId + in: query + description: Dedicated network id + schema: + $ref: '#/components/schemas/NetworkId' + - $ref: "#/components/parameters/x-device" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of existing device accesses to dedicated networks, optionally filtered for a given device and/or for a dedicated network (the list can be empty) + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkAccessInfo' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + post: + tags: + - Accesses + summary: Create a device access to a dedicated network with given configuration + description: | + **NOTE:** + - When the API allows usage of a two-legged access token and the invoker uses it, the optional `device` object shall be present. + operationId: createNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateNetworkAccess' + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Device access status callback + summary: "Device access status notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + It will be called upon change of the network access request status. + Currently only DEVICE_ACCESS_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + '201': + description: Successful creation of network access for a device + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkAccessInfo' + headers: + Location: + description: 'URL including the resource identifier of the newly created network access.' + required: true + schema: + type: string + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /accesses/{accessId}: + get: + tags: + - Accesses + summary: Get a device access to the dedicated network and its configuration + operationId: readNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:read + parameters: + - name: accessId + in: path + required: true + schema: + $ref: "#/components/schemas/AccessId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: A device access to the dedicated network with configuration + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkAccessInfo' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Accesses + summary: Delete a device access to the dedicated network + operationId: deleteNetworkAccess + security: + - openId: + - dedicated-network-accesses:accesses:delete + parameters: + - name: accessId + in: path + required: true + schema: + $ref: "#/components/schemas/AccessId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Successful deletion of a device access + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + x-device: + name: x-device + in: header + description: Device object represented in a header + Device object (#/components/schemas/Device") represented in a header. + It is serialized according to RFC 8941 as a structured field value where + the Device object is a dictionary, with the following additonal provisions + - property names are changed to lower case to comply with the RFC + - serializing property values must comply with the RFC depending on the type, and in particular + - if the property value is a string which contains only ASCII characters, the string can be serialized as String, + as per section 3.3.3 of the RFC + - if the property value is a string and contains non-ASCII characters, the string must be serialized as Byte Sequence using UTF-8 encoding, + as per section 3.3.5 of the RFC + schema: + type: string + example: 'phonenumber="+123456789"' + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + AccessId: + description: Network access id in UUID format + type: string + format: uuid + + NetworkId: + description: Network id in UUID format + type: string + format: uuid + + DeviceAccessStatus: + description: | + The current status of the device access. The status can be one of the following: + * `REQUESTED` - The Device Access is requested, but not granted. Possible transitions to GRANTED and DENIED states + * `GRANTED` - The Device Access is granted by the CSP, and the device can access the Dedicated Network when the network is in the ACTIVATED state. Possible transition to DENIED state + * `DENIED` - The Device Access is denied by the CSP, and the device can not access the Dedicated Network. The denial can be caused by a veriaty of conditions, such as lack of resources or system failure. + + type: string + enum: + - REQUESTED + - GRANTED + - DENIED + + ReasonInfo: + type: object + required: + - code + - message + properties: + code: + type: string + description: A human-readable code to describe the reason + message: + type: string + description: A human-readable description of what the reason represents + + DeviceAccessStatusInfo: + description: Additional information about the reason for the current device access status + type: object + properties: + reason: + allOf: + - $ref: "#/components/schemas/ReasonInfo" + - type: object + properties: + code: + enum: + - REQUEST_APPROVED + - REQUEST_REJECTED + - REQUEST_FAILED + - ACCESS_REVOKED + - ACCESS_FAILED + + BaseNetworkAccessInfo: + description: Common attributes of a device access to a dedicated network + type: object + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + device: + $ref: "#/components/schemas/Device" + qosProfiles: + description: (Optional) List of supported QOS profiles usable for the device. When absent, all QosProfiles of the Network are supported. Only a subset of the QOS profiles of the network is allowed + type: array + items: + type: string + minItems: 1 + defaultQosProfile: + description: (Optional) The default QOS profile of a device access. When absent, the defaultQosProfile of the Network is used + type: string + sink: + description: The address to which events shall be delivered using the selected protocol. + type: string + format: uri + pattern: ^https:\/\/.+$ + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + required: + - networkId + + CreateNetworkAccess: + description: Attributes required to create a dedicated network access for a device. + # NOTE this design prepares for adding request specific attributes later + allOf: + - $ref: "#/components/schemas/BaseNetworkAccessInfo" + + NetworkAccessInfo: + description: Information about a dedicated network access for a device + allOf: + - $ref: "#/components/schemas/BaseNetworkAccessInfo" + - type: object + properties: + id: + $ref: "#/components/schemas/AccessId" + status: + $ref: "#/components/schemas/DeviceAccessStatus" + statusInfo: + $ref: "#/components/schemas/DeviceAccessStatusInfo" + required: + - id + - status + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.dedicated-network.v0.device-access-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.dedicated-network-accesses.v0.device-access-status-changed: "#/components/schemas/EventDeviceAccessStatusChanged" + + EventDeviceAccessStatusChanged: + description: Event to notify a device access status change + type: object + properties: + data: + type: object + description: Status change details + required: + - accessId + - deviceAccess + properties: + accesskId: + $ref: "#/components/schemas/AccessId" + status: + $ref: "#/components/schemas/DeviceAccessStatus" + statusInfo: + $ref: "#/components/schemas/DeviceAccessStatusInfo" + required: + - data + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + - INCOMPATIBLE_STATE + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + GENERIC_409_INCOMPATIBLE_STATE: + description: A resource referenced in the request is in an incompatible state for the requested operation + value: + status: 409 + code: INCOMPATIBLE_STATE + message: A referenced resource is in an incompatible state. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + + DEVICE_ACCESS_STATUS_CHANGED_EXAMPLE: + summary: Device access status changed + description: Cloud event example for network status change to GRANTED + value: + id: 625b2d4b-4da7-4f07-9169-e60ffdf7667c + source: 'https://api.example.com/dedicated-network-accesses/v0/accesses/b69e5404-3871-448d-8f9f-11dc5d29a4c8' + specversion: '1.0' + type: "org.camaraproject.dedicated-network.v0.device-access-status-changed" + time: '2024-11-29T13:04:00Z' + data: + accessId: b69e5404-3871-448d-8f9f-11dc5d29a4c8 + status: GRANTED + statusInfo: + code: REQUEST_APPROVED + message: The device access request is approved. diff --git a/original/DedicatedNetworks/code/API_definitions/dedicated-network-areas.yaml b/original/DedicatedNetworks/code/API_definitions/dedicated-network-areas.yaml new file mode 100644 index 0000000000000000000000000000000000000000..0291d9cd9124de28f8dfd94f9eb35e72fc44c64e --- /dev/null +++ b/original/DedicatedNetworks/code/API_definitions/dedicated-network-areas.yaml @@ -0,0 +1,433 @@ +openapi: 3.0.3 +info: + title: Dedicated Network - Areas + description: | + + # Introduction + + This API allows for discovering available network service areas, which are the geographical areas offered by the network provider where consitent coverage according to indicated network profile(s) and QoS profiles is provided, and which is to be used in conjunction with the Dedicated Network API. + + For more information about the Dedicated Network APIs, see the _GeneralDescription_ document in the Dedicated Networks [repository](https://github.com/camaraproject/DedicatedNetworks/). + + # Network Service Areas + + A Network Service Area represents a geographical area with coverage consistent with the characteristics of the network profiles and the QoS profiles supported in the area. It enables API Consumers to select the geographical area where they can expect to consume the reserved network connectivity resources. A Network Service Area may have been pre-agreed between the API Provider and API Consumer. + + A Network Service Area contains information about its geographical boundaries and the supported network profiles and QoS profiles. It is uniquely identified by a UUID identifier and it contains a human readable name and description. + + # Network Service Areas API + + The key characteristics of the API include: + + - Network Service Areas are read-only resources from the API Consumer perspective + + - They are discoverable by POST operations + + - They are readable by GET operations + + - Each Network Service Area has a unique identifier (areaId) + + - The areaId serves as a reference when creating a Dedicated Network + + - The API returns only Network Service Areas that the API Consumer is eligible to use based on their agreements + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Querying one or more Areas + + All available network service areas of the API consumer can be queried by performing a `POST` operation on the `/retrieve-service-areas` endpoint. + + The API Consumer may provide the following input parameters as search criteria which must be matched for the network service area to be returned: + + - `atLocation` - to return the network service areas available at the given geographical location + + - `overlappingArea` - to return the network service areas whose geographical area overlaps (but does not fully cover) the input geographical area, where the input geographical area may be a circle or polygon + + - `coveringArea` - to return the network service areas whose geographical area fully covers the input geographical area will be returned, where the input geographical area may be a circle or polygon + + - `byName` - to return the network service areas with a name matching exactly the input string + + - `byNetworkProfileId` - to return the network service areas which support the input network profile identifier + + - `byQosProfileName` - to return the network service areas which support the input QoS profile name + + A specific network service area of the API consumer can be queried by performing a `GET` operation on the `/areas/{areaId}` endpoint. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +servers: + - url: "{apiRoot}/dedicated-network-areas/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /retrieve-service-areas: + post: + tags: + - Areas + summary: Retrieve dedicated network service areas, filtered by additional search criteria + operationId: retrieveNetworkServiceAreas + requestBody: + description: Parameters to query service areas + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveServiceAreasRequest" + required: true + responses: + '200': + description: List of available dedicated network service areas + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/ServiceArea' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + /areas/{areaId}: + get: + tags: + - Areas + summary: Read a dedicated network service area + operationId: readNetworkServiceArea + parameters: + - name: areaId + in: path + required: true + schema: + $ref: "#/components/schemas/ServiceAreaId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Information about the dedicated network service area + content: + application/json: + schema: + $ref: '#/components/schemas/ServiceArea' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkProfileId: + type: string + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ServiceAreaId: + type: string + format: uuid + + RetrieveServiceAreasRequest: + description: Request object to retrieve service areas that match all the given properties + type: object + properties: + atLocation: + $ref: "#/components/schemas/Point" + overlappingArea: + $ref: "#/components/schemas/Area" + coveringArea: + $ref: "#/components/schemas/Area" + byName: + type: string + byNetworkProfileId: + $ref: "#/components/schemas/NetworkProfileId" + byQosProfileName: + $ref: "#/components/schemas/QosProfileName" + + ServiceArea: + description: Common attributes of a service area, i.e. where the dedicated network service is supported + properties: + id: + $ref: '#/components/schemas/ServiceAreaId' + name: + type: string + description: + type: string + area: + $ref: '#/components/schemas/Area' + networkProfiles: + description: Dedicated network profiles which are supported in this area. + type: array + items: + $ref: "#/components/schemas/NetworkProfileId" + minItems: 1 + qosProfiles: + description: Qos Profiles which are supported in this area. + type: array + items: + $ref: '#/components/schemas/QosProfileName' + minItems: 1 + required: + - id + - area + anyOf: + - required: + - networkProfiles + - required: + - qosProfiles + + Area: + description: Common attributes of a geographical area, base schema for all area types + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + description: | + Radius from `center` in meters. + minimum: 1 + maximum: 200000 + required: + - center + - radius + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map. + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location. + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location. + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. diff --git a/original/DedicatedNetworks/code/API_definitions/dedicated-network-profiles.yaml b/original/DedicatedNetworks/code/API_definitions/dedicated-network-profiles.yaml new file mode 100644 index 0000000000000000000000000000000000000000..1f79902cc7535cda3894c469b62e098417fa99b6 --- /dev/null +++ b/original/DedicatedNetworks/code/API_definitions/dedicated-network-profiles.yaml @@ -0,0 +1,402 @@ +openapi: 3.0.3 +info: + title: Dedicated Network - Network Profiles + description: | + + # Introduction + + This API allows for discovering available network profiles, which are offered by the network provider to be used in conjunction of the Dedicated Network API. Network profiles describe the capabilities and performance targets of a dedicated network. For more information about the Dedicated Networks APIs, see [link](). + + # Network Profiles + + A Network Profile represents a predefined set of network capabilities and performance characteristics that can be applied when creating a Network. It enables API Consumers to understand the capabilities they can expect when using the reserved network connectivity resources. A Network Profile is a validated, supported configuration that has been pre-approved between the API Provider and API Consumer. + + A Network Profile contains information about the maximum number of devices allowed, the aggregated throughput to be provided, and a set of allowed QoS Profiles that devices can use when having access to the Dedicated Network. The concept of named QoS Profiles is re-used from the [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) API family. An API provider may offer the QualityOnDemand `qos-profiles` API for resolving a QoS Profile name into characteristics of a specific QoS profile. + + Network Profiles are designed to support different use-cases and should contain the matching `qos-profile` combinations. Generally, two types of Network Profiles can be identified + * Network Profiles containing only a `defaultQosProfile` + * Network Profiles containing one or more additional `qos-profile`s with the `qosProfiles` array. When multiple QoS Profiles are supported within one Network Profile, the QualityOnDemand `quality-on-demand` API may be used to assign one of the available QoS profiles to a specific device while the Network is in `ACTIVATED` state + + Devices are not neccessarily using connectivity continuously. The value of the `maxNumberOfDevices` parameter should be set _generous_, considering that not all devices using connectivity simultaneously and/or continuously. + + The parameters `aggregatedUlThroughput` and `aggregatedDlThroughput` define the (hard) limits of simultaneous connectivity usage, ie. sum of all traffic pertaining all devices using the available QoS profiles. + + A detailed description of the individual parameters may be included within the _terms and conditions_ (outside of scope for the API). + + # Network Profiles API + + The key characteristics of the API include: + + - Network Profiles are read-only resources from the API Consumer perspective + + - They are discoverable through GET operations + + - Each Network Profile has a unique identifier (profileId) + + - The profileId serves as a reference when creating a Dedicated Network + + - The API returns only Network Profiles that the API Consumer is eligible to use based on their agreements + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network-profiles/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /profiles: + get: + tags: + - Profiles + summary: Read dedicated network profiles + operationId: readNetworkProfiles + security: + - openId: + - dedicated-network-profiles:profiles:read + parameters: + - name: name + in: query + description: name of a network profile + schema: + type: string + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of available network profiles + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkProfile' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /profiles/{profileId}: + get: + tags: + - Profiles + summary: Read a dedicated network profile + operationId: readNetworkProfile + security: + - openId: + - dedicated-network-profiles:profiles:read + parameters: + - name: profileId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkProfileId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of available network profiles + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkProfile' + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkProfileId: + description: Network profile id in UUID format + type: string + format: uuid + + NetworkProfile: + type: object + properties: + id: + $ref: '#/components/schemas/NetworkProfileId' + name: + description: A human-readable name to describe the network profile + type: string + maxNumberOfDevices: + type: integer + aggregatedUlThroughput: + $ref: "#/components/schemas/BitRate" + aggregatedDlThroughput: + $ref: "#/components/schemas/BitRate" + qosProfiles: + description: Qos Profiles, which are supported by the dedicated network. + type: array + items: + $ref: '#/components/schemas/QosProfileName' + minItems: 1 + defaultQosProfile: + $ref: '#/components/schemas/QosProfileName' + required: + - id + - maxNumberOfDevices + - aggregatedUlThroughput + - aggregatedDlThroughput + - qosProfiles + - defaultQosProfile + + BitRate: + description: Specification of bitrate + type: object + properties: + value: + description: Quantity of bitrate + type: integer + example: 10 + format: int32 + minimum: 1 + maximum: 1024 + unit: + $ref: "#/components/schemas/BitRateUnitEnum" + + BitRateUnitEnum: + description: Units of bitrate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. diff --git a/original/DedicatedNetworks/code/API_definitions/dedicated-network.yaml b/original/DedicatedNetworks/code/API_definitions/dedicated-network.yaml new file mode 100644 index 0000000000000000000000000000000000000000..cf15b3ad807488ee1d0fcbdf99a910c82a1c0538 --- /dev/null +++ b/original/DedicatedNetworks/code/API_definitions/dedicated-network.yaml @@ -0,0 +1,702 @@ +openapi: 3.0.3 +info: + title: Dedicated Network - Networks + description: | + This API allows for requesting a Dedicated Network, which provides a set of capabilities and connectivity performance targets. The Dedicated Network may be requested for a particular geographical location and at a particular time window. Depending on the requested start time for the dedicated network, the network may first enter a _reserved_ state. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Creating a network + + A network is created by performing a `POST` operation on the `/networks` endpoint. + + The API Consumer needs to provide the following input parameters to create a network: + + - the chosen Network Profile (networkProfileId) or QoS profile (qosProfileName). The choice is between a Network Profile (which contains properties like maximum number of devices, aggregated throughput, a list of supported QOS profiles, and a default QoS profile) and a QoS Profile which is equivalent to a simplified Network Profile for a single device, with just a default QoS profile, and with the aggregated throughput corresponding to the throughput defined by the QoS Profile. + + - the Service Area (serviceAreaId) + + - the service start and end times (Service Time). + + - Optionally, callback related information through sink and sinkCredential parameters to receive notifications about the lifecycle events of the network. + + The API returns a networkId. The networkId is a unique identifier of the network, which remains unchanged during its lifetime. The networkId is required when creating Device Accesses. + + Initially, the created network is in `REQUESTED` state. The network is only usable when the network is in `ACTIVATED` state. Find a detailed description of the network states [here](). + + + # Querying one or more Networks + + All available network of the API consumer can be queried by performing a `GET` operation on the `/networks` endpoint. + + A specific network of the API consumer can be queried by performing a `GET` operation on the `/networks/{networkId}` endpoint, where the networkId has been obtained during the _create_ procedure. + + # Deleting a Network + + A specific network of the API consumer can be deleted by performing a `DELETE` operation on the `/networks/{networkId}` endpoint. Deletion of a network can be interpreted as a cancellation of the resource reservation. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DedicatedNetworks +servers: + - url: "{apiRoot}/dedicated-network/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Networks + description: Manage a dedicated network +paths: + /networks: + get: + tags: + - Networks + summary: Get a list of dedicated networks + operationId: listNetworks + security: + - openId: + - dedicated-network:networks:read + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: List of dedicated networks (the list can be empty) + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/NetworkInfo' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + post: + tags: + - Networks + summary: Request to create a dedicated network + operationId: createNetwork + security: + - openId: + - dedicated-network:networks:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateNetwork' + parameters: + - $ref: "#/components/parameters/x-correlator" + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Network status callback + summary: "Network status notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + It will be called upon change of the network request status. + Currently only NETWORK_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + NETWORK_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/NETWORK_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + '201': + description: Reception acknowlegement a dedicated network request + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkInfo' + headers: + Location: + description: 'URL including the resource identifier of the newly created dedicated network.' + required: true + schema: + type: string + format: uri + '400': + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /networks/{networkId}: + get: + tags: + - Networks + summary: Get the current information about a dedicated network + operationId: readNetwork + security: + - openId: + - dedicated-network:networks:read + parameters: + - name: networkId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkId" + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Current dedicated network information + content: + application/json: + schema: + $ref: '#/components/schemas/NetworkInfo' + '400': + $ref: "#/components/responses/Generic400" + '404': + $ref: "#/components/responses/Generic404" + delete: + tags: + - Networks + summary: Delete a dedicated network + operationId: deleteNetwork + security: + - openId: + - dedicated-network:networks:delete + parameters: + - name: networkId + in: path + required: true + schema: + $ref: "#/components/schemas/NetworkId" + - $ref: "#/components/parameters/x-correlator" + responses: + '204': + description: Successful deletion of a dedicated network + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network id in UUID format + type: string + format: uuid + + NetworkProfileId: + description: Network profile id in UUID format + type: string + format: uuid + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the QoS Profile API. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + ServiceAreaId: + type: string + format: uuid + + BaseNetworkInfo: + description: Common attributes of a dedicated network + type: object + properties: + networkProfileId: + $ref: '#/components/schemas/NetworkProfileId' + qosProfileName: + $ref: '#/components/schemas/QosProfileName' + serviceTime: + $ref: '#/components/schemas/ServiceTime' + serviceAreaId: + $ref: '#/components/schemas/ServiceAreaId' + sink: + description: The address to which events shall be delivered using the selected protocol. + type: string + format: uri + pattern: ^https:\/\/.+$ + sinkCredential: + $ref: '#/components/schemas/SinkCredential' + required: + - serviceTime + - serviceAreaId + oneOf: + - required: + - networkProfileId + - required: + - qosProfileName + + NetworkInfo: + description: Current dedicated network information + allOf: + - $ref: "#/components/schemas/BaseNetworkInfo" + - type: object + properties: + id: + $ref: '#/components/schemas/NetworkId' + status: + $ref: '#/components/schemas/NetworkStatus' + required: + - id + - status + + CreateNetwork: + description: Attributes required to create a dedicated network + # NOTE this design prepares for adding request specific attributes later + allOf: + - $ref: "#/components/schemas/BaseNetworkInfo" + + NetworkStatus: + description: | + The current status of the requested network. The status can be one of the following: + * `REQUESTED` - The DN is requested, but not approved. Possible transitions to RESERVED, ACTIVATED and TERMINATED states + * `RESERVED` - Request is accepted by the CSP (CSP has committed the requested resources), but the Network cannot be used (outside of requested time-window) + * `ACTIVATED` - Network turns from reserved into Activated. Now, devices with access can use the network. Possible transitions to RESERVED or TERMINATED states + * `TERMINATED` - The Network resource is used and up for deletion. The API does not allow any action (except delete). + + type: string + enum: + - REQUESTED + - RESERVED + - ACTIVATED + - TERMINATED + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.dedicated-network.v0.network-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow RFC 3339 + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.dedicated-network.v0.network-status-changed: "#/components/schemas/EventNetworkStatusChanged" + + EventNetworkStatusChanged: + description: Event to notify a network status change + type: object + properties: + data: + type: object + description: Status change details + required: + - networkId + - status + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + status: + $ref: "#/components/schemas/NetworkStatus" + required: + - data + + ServiceTime: + type: object + properties: + start: + type: string + format: date-time + description: It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + end: + type: string + format: date-time + description: It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + required: + - start + - end + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: REQUIRED. An absolute UTC instant at which the token shall be considered expired. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + examples: + + NETWORK_STATUS_CHANGED_EXAMPLE: + summary: Network status changed + description: Cloud event example for network status change to ACTIVATED + value: + id: 625b2d4b-4da7-4f07-9169-e60ffdf7667c + source: 'https://api.example.com/dedicated-network/v0/networks/b69e5404-3871-448d-8f9f-11dc5d29a4c8' + specversion: '1.0' + type: "org.camaraproject.dedicated-network.v0.network-status-changed" + time: '2024-11-29T13:04:00Z' + data: + networkId: 'b69e5404-3871-448d-8f9f-11dc5d29a4c8' + status: 'ACTIVATED' diff --git a/original/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md b/original/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md new file mode 100644 index 0000000000000000000000000000000000000000..371682d60d94ae46e2a9a32ba86b32f670aa2643 --- /dev/null +++ b/original/DedicatedNetworks/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md @@ -0,0 +1,241 @@ +# High level description of Dedicated Networks concept and APIs +## Introduction +_Dedicated Networks_ enable dedicated use of public network connectivity resources by reserving some of these resources for use by devices and applications. To these devices and applications, the reserved resources appear as their own virtual or logical network. Please check [here](https://github.com/camaraproject/DedicatedNetworks/blob/r1.1/documentation/SupportingDocuments/UsageScenarios.md) for several usage scenarios for Dedicated Networks. + +Fixed and Mobile Networks already offer the capability of separating devices into different networks. These concepts are sometimes called logical networks or virtual private networks. Multiple of these networks can coexist on the same physical network and can separate target traffic from other traffic for assured performance, enhanced security and other scenarios where consistent experience is required. + +There are different options to technically realize a Dedicated Network. For example: + +- Using 5G Network Slices (see 3GPP 23.501 Rel-15, clause 5.15) + +- Using 5G Non-Public Networks (NPN), specifically the Public Network Integrated NPN (PNI-NPN), see 3GPP 23.501 Rel-16, clause 5.30) + +- Using a separate 4G APN (see 3GPP 23.401 Rel-8) or 5G DNNs (see 3GPP 23.501 Rel-15). Note, a DNN is equivalent to an APN, per 3GPP 23.003 Rel-15. + +Dedicated Networks abstract the complexity across **Network Provider** realizations to enable coherent use of diverse network capabilities. + +A Dedicated Network is often only needed for a specific time duration (e.g. one hour) and at specific locations (e.g. the area of a festival). These are referred to as Service Time and Service Area. + +The CAMARA Dedicated Network APIs allow **API Consumers** to programmatically manage Dedicated Networks, without the need for in-depth knowledge of telecommunications systems. + +API Consumers have control over which devices are allowed to access and use the reserved network connectivity resources. In addition, network connectivity characteristics, for example, routing and performance may be individually tailored for each device. + +Detailed characteristics, behaviors and costs pertaining to Dedicated Networks are typically described by the **API Provider** in the terms and conditions. Such terms and conditions may also contain obligations and restrictions. + +An API Provider realizes Dedicated Networks based on the physical network resources managed by a Network Provider. An API Provider can be the Network Provider. + +The present set of [Usage Scenarios](../SupportingDocuments/UsageScenarios.md) focuses on B2B use-cases, where the owner of the devices / device subscriptions is also acting as API invoker for the Networks and the Accesses APIs. This constellation allows using using the MSISDN as device identifier with a two-legged access tokens, since no additional consent needs to be obtained. + + +**Key roles** + +| **Role Name** | **Description** | +| ---- | ------- | +| API Consumer | The entity that consumes the Dedicated Network APIs | +| API Provider | The entity that provides the Dedicated Network APIs | +| Network Provider | The entity that provides the physical network resources | + +## Dedicated Network APIs + +The CAMARA Dedicated Network APIs allow for programmatic management of Dedicated Networks, without the need for in-depth knowledge of telecommunications systems. + +The APIs are summarized in the table below followed by a brief description. Detailed descriptions are provided within each specification. + +| **API** | **Purpose of the API** | **Key Abstractions and concepts** | +| ---- | ------- | ----| +| Dedicated Network API | Reservation and lifecycle management of network connectivity resources for dedicated use. | A Dedicated Network is a logical resource and is used to embody the reservation of network connectivity resources in the physical network. Initiating a new reservation request using this API results in a new Dedicated Network resource being created. The Dedicated Network undergoes various lifecycle States including REQUESTED, RESERVED, ACTIVATED and TERMINATED. Reservation of resources occurs based on the selected Network Profile, duration when the reservation is needed (Service Time) and geographical areas where the service is needed (Service Area). | +| Dedicated Network Profiles API | Discovery of predefined set of network capabilities and performance characteristics | A Network Profile represents a predefined set of network capabilities and performance characteristics that can be applied when creating dedicated networks. Each profile represents a validated, supported configuration that has been pre-approved in the _terms and conditions_ between the API Provider and API Consumer. | +| Dedicated Network Areas API | Discovery of network service areas with support for network profiles and QoS profiles | A Network Service Area represents a geographical area with coverage consistent with one or more network profiles and/or one or more QoS profiles. It enables API Consumers to select the geographical area where they can expect to consume the reserved network connectivity resources. A Network Service Area may have been pre-agreed between the API Provider and API Consumer in the _terms and conditions_ between the API Provider and API Consumer. | +| Dedicated Network Accesses API | Managing access to the Dedicated Network, i.e., controlling which devices may benefit from the reserved resources and capabilities | A Device Access represents the permission for a specific device to use a Dedicated Network's reserved connectivity resources. The usage of resources can be tailored to each device within the constraints of the applicable Network Profile.
                                                          The access for devices to the network can only be managed when the Network is created and not in the TERMINATED [state](#states-of-the-network). | + +The Accesses and the Network Profile re-use the concept of named QoS Profiles from [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) for describing connectivity performance characteristics. An API provider may offer the `qos-profiles` API for resolving a QoS Profile name into characteristics of a specific QoS profile. + +When multiple QoS profiles are defined within a Network Profile, the API Consumer may either statically assign a different QoS profile (from the set of QoS profiles) for each device access or may dynamically create QoS Sessions using the QualityOnDemand `quality-on-demand` API. +The API Consumer may also restict the list of possible QoS Profiles within a Device Access. + +A high-level sequence of steps involved when using Dedicated Network APIs is depicted in the diagram below and further described in their respective sections. + +**Figure**: High-level sequence of steps
                                                          + +```mermaid + graph TD + 0[Complete Pre-requisites] + 1[Choose Dedicated Network Service Area] + A[Choose Dedicated Network Profile or QoS Profile] + B[Create a Dedicated Network] + C[Create Device Accesses] + D[Allowed devices can use reserved network connectivity resources] + 0 --> 1 + 1 --> A + A --> B + B --> C + C --> D +``` + +## Pre-requisites + +Before Dedicated Network APIs can be invoked, relevant agreements need to be in place between the API Consumer and the API Provider. Conceptually, the agreement contains all the different terms and conditions, which typically include price, service descriptions and conditions. It also includes obligations and restrictions possibly for both, the API Provider and the API Consumer, etc. + +An API Provider may provide a catalog where API Consumers can get an overview of the various options available. For example, there may be a catalog of available APIs, and a catalog of available parameter sets for each of the APIs. + +The API Provider may also offer a procedure for requesting additional customization, for example, additional Service Areas or Network Profiles. Such a procedure can leverage conventional methods such as emails or phone conversations. + +API Consumers selects from available Network Profiles, QoS profiles, and Service Areas offered by the API Provider which then become part of the agreed terms and conditions. + +This preparation phase is **outside the scope** of the Dedicated Network APIs. + +As result of the agreement on the terms and conditions, the following aspects are determined + +- URLs and credentials for the API Consumer to use + +- A set of capabilities and performance targets (Network Profiles and QoS Profiles) that an API Consumer is eligible to use + +- A set of geographic areas (Service Areas) that an API Consumer is eligible to use + +- The API Consumer is aware about the terms and conditions (incl price), when selecting different parameter or parameter combinations according to the conditions. + +Note that, at completion of the pre-requisites, no network connectivity resources are reserved, i.e., no Dedicated Network is created. + +## Detailed high-level flow +The diagram below attempts to depict the complete flow including API endpoint, response codes, and key parameters. + +**Figure**: High Level Flow with additional details +```mermaid + +sequenceDiagram + participant App as API Consumer (Application) + participant P as Profiles API + participant A as Areas API + participant N as Networks API + participant A as Accesses API + participant Network as Physical Network + participant D as Device(s) + Note over App,D: Pre-requisites completed + + rect rgba(51, 49, 49, 0.6) + note right of App: 1: Reading Profiles + App->>P: GET /profiles + P->>App: 200 OK (Profiles [profileId, ...]) + end + + rect rgba(51, 49, 49, 0.6) + note right of App: 2: Discovering Areas + App->>P: POST /retrieve-service-areas + P->>App: 200 OK (Service areas [areaId, ...]) + end + + rect rgba(51, 49, 49, 0.6) + note right of App: 3: Creating a Dedicated Network + App->>N: POST /networks (profileId or qosProfileName, areaId, serviceTime, ...) + N->>App: 201 Created (networkId, status=REQUESTED, ...) + N <<-->> Network: Provisioning / configuration as needed
                                                          Managed by API Provider and Network Provider
                                                          Outside scope of the Dedicated Network APIs + alt Callback enabled + N-->>App: Optional callback: (networkId, status=RESERVED) + N-->>App: Optional callback: (networkId, status=ACTIVATED) + else Polling + App->>N: GET /networks/{networkId} + N-->>App: 200 OK (networkId, status=ACTIVATED) + end + end + rect rgba(51, 49, 49, 0.6) + note right of App: 4: Managing Device Access + loop Create Access resource for a given device to the given network + App->>A: POST /accesses (networkId, device) + A->>App: 201 Created (accessId, status=REQUESTED) + end + alt Callback enabled + N-->>App: Optional callback: (accessId, status=GRANTED) + else Polling + App->>N: GET /accesses/{accessId} + N-->>App: 200 OK (accessId, status=GRANTED) + end + A <<-->> Network: Provisioning / configuration as needed
                                                          Managed by API Provider and Network Provider
                                                          Outside scope of the Dedicated Network APIs + loop Delete a previously created Access resource + App->>A: DELETE /accesses (accessId) + A->>App: 204 No Content + end + end + Note over App,D: 4: Dedicated Network in ACTIVATED state + loop One or more devices in GRANTED state + D-->>Network: Connect to network + Network-->>D: Connection established / denied + end +``` + +Description of main steps +1. Reading Profiles: The API Consumer is reading the eligible Network Profiles. Each Network Profile contains properties, like aggregated throughput or QoS profiles. Reading of the eligible QoS Profiles may also occur in this step (not shown in the diagram). + * The terms and conditions (see [Pre-requisites](#pre-requisites)) may define the conditions, constrains, etc for using the profile. +1. Discovering Areas: The API Consumer is retrieving the eligible Network Service Areas. Each Network Service Area contains properties, like the areas's geographical coordinates and supported network profiles and QoS profiles. + * The terms and conditions (see [Pre-requisites](#pre-requisites)) may define the conditions, constrains, etc for using the service area. +1. Creating a Dedicated Network: The API Consumer creates a network, providing the network profile or QoS profile, service time and service area as input parameters + * The network is initially in REQUESTED state. See [network lifecycle](#states-of-the-network) for more information. + * The API Consumer can register a sink for receiving network state changes. +1. Managing Device Access: The API Consumer may allow one or more devices to get access to the capabilities and pcapacity of the network + * The API Consumer may use the Accesses API, while the network is either in REQUESTED, RESERVED or ACTIVATED state. The API Consumer gets an error code, when using the Accesses API with a Network in TERMINATED state. + * Creating an Access resource corresponds to giving access for a device to the network. + * Deleting an Access resource corresponds to revoking access for a device to the network. +1. When Dedicated Network is in ACTIVATED state: Devices with access will be able to connect to the network. + * When a single QoS profile is used or a default QoS profile is defined within the Network Profile (or changed via the Access resources), all the traffic of the device will be treated with this QoS profile as default + * When multiple QoS profiles are defined within the Network Profile (or changed via the Access resources), the API Consumer may use the QOD API for managing QoS Sessions with the QoS Profiles listed in the Network Profile. + +## States of the network + +The dedicated network supports multiple states, i.e. REQUESTED, RESERVED, ACTIVATED and TERMINATED. The networks resource is created with a POST on the /networks API. The status of the HTTP resource is independent of the status of the representing dedicated network. + +On successful acceptance of the request, an HTTP resource is created. The response always returns a REQUESTED State. Reserved resources are only usable when the network is in ACTIVATED state. + +**Figure**: lifecycle of a network + +```mermaid +stateDiagram-v2 + [*] --> REQUESTED: POST /networks + REQUESTED --> RESERVED: Use is confirmed (Service Time not reached) + RESERVED --> ACTIVATED: Service Time reached + ACTIVATED --> TERMINATED: Service Time expires + REQUESTED --> ACTIVATED: Use is confirmed (Service Time already reached) + RESERVED --> TERMINATED: Failed to reserve resources +``` + +Explainations +- A network in REQUESTED state is not (yet) committed by the Network Provider. + +- A network in RESERVED state is committed to be available for use during the Service Time by the Network Provider. + +- The targeted resources of the network are free to be used by other users or for other purposes, while the network is in RESERVED state. + +- Reserved resources are only usable when the network is in ACTIVATED state. + +- The network may enter the ACTIVATED state directly after the REQUESTED state if the service start time has been reached when the API Provider successfully completed the resource reservation. + +- The network may enter the TERMINATED state directly after the REQUESTED state if the API Provider could not complete the resource reservation. + +- A network in TERMINATED state cannot be modified anymore and should be deleted. If not deleted by the API Consumer, the representing HTTP resource (URL) may be removed by the API Provider. + +## States of device access to the network + +The device access to the dedicated network supports multiple states, i.e. REQUESTED, GRANTED, and DENIED. The networks access resource is created with a POST on the /accesses API. It contains `deviceAccess` object which contains the state information of the device access. + +On successful acceptance of the request, an HTTP resource is created. The response always returns a REQUESTED State. Reserved resources are only usable when the network is in ACTIVATED state. + +**Figure**: lifecycle of a device access to network + +```mermaid +stateDiagram-v2 + [*] --> REQUESTED: POST /accesses + REQUESTED --> GRANTED: Device Access is granted + REQUESTED --> DENIED: Device Access is rejected or it failed + GRANTED --> DENIED: Device Access is revoked (after having been granted) or it failed. +``` + +Explainations +- A device access is usable only when it is in GRANTED state while the dedicated network is in ACTIVATED state. + +- A device access will transition from REQUESTED to GRANTED state (with reason code: REQUEST_APPROVED) when the access to the network is approved. + +- A device access will transition from REQUESTED to DENIED state (with reason code: REQUEST_FAILED) if failure occured while approving the request. + +- A device access will transition from REQUESTED to DENIED state (with reason code: REQUEST_REJECTED) if the request is rejected. + +- A device access will transition from GRANTED to DENIED state (with reason code: ACCESS_FAILED) if failure occured after the access has been granted. + +- A device access will transition from GRANTED to DENIED state (with reason code: ACCESS_REVOKED) when the grant to access the network is revoked. diff --git a/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist.md b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..239bcb4ed7d1cdfb6de61f47ca3f12b1e5e72e17 --- /dev/null +++ b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network.yaml](/code/API_definitions/dedicated-network.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist.md b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..2c898a213194185ee088f543cc288e7b6694697a --- /dev/null +++ b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-accesses-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network-accesses v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network-accesses.yaml](/code/API_definitions/dedicated-network-accesses.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist.md b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..1fa4133f7646113aafdd178c73c96e4fde1ed17a --- /dev/null +++ b/original/DedicatedNetworks/documentation/API_documentation/dedicated-network-profiles-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for dedicated-network-profiles v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/dedicated-network-profiles.yaml](/code/API_definitions/dedicated-network-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | [/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md](/documentation/API_documentation/DedicatedNetworks_GeneralDescription.md) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/227934209/DedicatedNetworks+APIs+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DedicatedNetworks/documentation/SupportingDocuments/README.MD b/original/DedicatedNetworks/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DedicatedNetworks/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios.md b/original/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios.md new file mode 100644 index 0000000000000000000000000000000000000000..7c7412768333df9bb717586e6a6fa0c394edc9b7 --- /dev/null +++ b/original/DedicatedNetworks/documentation/SupportingDocuments/UsageScenarios.md @@ -0,0 +1,60 @@ +# Usage Scenarios of the Dedicated Networks API + +## Introduction + +The API was motivated by a number of use cases and usage scenarios during the API presentation ([pdf](https://github.com/camaraproject/APIBacklog/blob/main/documentation/SupportingDocuments/DedicatedNetworks%C2%A0API%C2%A0Introduction.pdf)). A short description is provided in the following. + +## Media Production + +A Media Producer needs a stable connectivity performance for a camera crew with two or more cameras for capturing the live video footage of a press briefing event. Although multiple cameras are actively used during the production, only a single live video stream is produced. The different cameras are positioned to capture different aspects of the press briefing, for example, one camera is capturing all speakers (pan view) and another camera is capturing individual speakers (head and shoulder). The program director selects the camera (called “Live Camera”), which is feeding the outgoing live video stream. For the selection, the video stream of each camera is shown at a production gallery to the production director. + +Each camera should get the needed connectivity performance (in terms of throughput) during the press briefing event. Standby Cameras (cameras, which are only streaming the video to the production gallery) can have a lower quality and lower QOS. The live camera (camera, which is currently feeding the outgoing video stream) should have a higher quality and higher QOS. The used QOS profile is changed dynamically for each camera. + +The media producer is planning the video production of the press briefing before the press briefing event. It should be assumed that the media producer is already an API customer of the Network Provider and has access to the Dedicated Network API. The Network is prepared with the needed configurations, like QOS Profile configurations. + +The media producer decides on the used cameras before the press briefing. It should be assumed that the media producer has access to a pool of cameras, including video encoding and transmission equipment, and only a subset of cameras are used within a certain production event. Each camera is equipped with a matching SIM for the Network Provider. The media producer permits devices (SIMs), which should get access to the capabilities provided by the Dedicated Network. + +## Festival + +The festival organizer is interested in obtaining a dedicated network from a public network provider to connect multiple devices for “running” a festival. Thus, the dedicated network is not intended for the festival audience/visitors. The stable connectivity performance provided by the dedicated network is needed for operating credit card readers (festival payment system) and for the CCTV (security) cameras. The quality of the CCTV cameras can be switched between “matrix view” (low quality for each camera) and “single view” (high quality for the single camera). An according QOS profile is selected as needed. + +The festival organizer is planning the festival, e.g., how many credit card readers & CCTV cameras are needed. The festival organizer knows, “where” (location) and “when” (time) the festival will be and is interested in getting a dedicated network for enabling the festival. + +It should be assumed that the festival organizer is already an API customer of the Network Provider and has access to the Dedicated Network API. Each device is equipped with a matching SIM for the Network Provider. It should be assumed that the festival organizer has more devices/SIMs and only uses a subset of these devices. The festival organizer permits devices (SIMs), which should get access to the capabilities provided by the Dedicated Network. + +## Enterprise + +A dedicated network is used to connect devices (e.g., Laptops) of employees to corporate services. Different connectivity quality (QOS Profiles) is needed, e.g., during a video conference/virtual meeting. During a virtual meeting, one or more meeting participants may decide to switch on the video camera in addition to the audio streams, to improve the meeting quality. + +The Enterprise wants secure access to its corporate services and is planning the needed capacity. The devices are managed by the enterprise IT organization. It should be assumed that the enterprise is already an API customer of the Network Provider, which offers the Dedicated Network API. Each device is equipped with a matching SIM for the Network Provider. The enterprise permits only its own devices (SIMs) to get access to the capabilities provided by the Dedicated Network. + +## Additional Scenarios + +Here are the other Dedicated Network use cases they can be added to the list: + +- **Emergency Services**: Dedicated Networks provide reliable communication and data services for emergency responders, ensuring they have the necessary information and connectivity during critical situations. + +- **Smart Cities**: Dedicated Networks support intelligent transport systems, public safety, and other smart city applications. +The following use cases from 3-12 can be added under the Enterprise section. + +- **Airports**: Dedicated Networks can be used for video surveillance, asset tracking, and real-time data analytics to enhance security and operational efficiency. + +- **Mining**: In the mining industry, Dedicated Networks support remote control of machinery, environmental monitoring, and predictive maintenance. + +- **Manufacturing and Logistics**: Dedicated Networks enable the use of Automated Guided Vehicles (AGVs), robots, and drones for efficient operations. They also support asset tracking and real-time data analytics. + +- **Ports**: Dedicated Networks facilitate the management of logistics and supply chains, ensuring smooth operations and tracking of assets. + +- **Oil & Gas**: Dedicated Networks are used for environmental monitoring, asset tracking, and ensuring safety in operations. + +- **Utilities**: Dedicated Networks support the monitoring and management of utility services, enhancing reliability and efficiency. + +- **Rail**: Dedicated Networks are used for asset tracking, remote control of machinery, and real-time data analytics to improve safety and efficiency in rail operations + +- **Healthcare**: In hospitals, Dedicated Networks ensure secure and reliable connectivity for life-saving systems and medical devices. + +- **Public Venues**: In large public venues like stadiums and convention center's, Dedicated Networks provide predictable connectivity and enhanced security for various applications. + +- **Industrial Applications**: Dedicated Networks support robotics, automated inventory control, and other industrial applications that require constant connectivity and low latency. + +- **Transportation and Logistics**: Dedicated Networks facilitate the tracking and management of assets, ensuring efficient operations in transportation and logistics. \ No newline at end of file diff --git a/original/DeviceAuthenticity/README.md b/original/DeviceAuthenticity/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9ff1e7a6ee8b9d48de41fe4b64c3db906e500680 --- /dev/null +++ b/original/DeviceAuthenticity/README.md @@ -0,0 +1,43 @@ + + + + + + + + + +# DeviceAuthenticity + +Sandbox API Repository to describe, develop, document, and test the DeviceAuthenticity Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/czLe) + +## Scope + +* Service API(s) “DeviceAuthenticity” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * Determine whether a given device associated with the provided device identifier is subject to any restrictions or risk flags. + * Provide a clear overall status describing the device’s condition. +* Describe, develop, document, and test the API(s) +* Started: **December 2025** + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually together with the DeviceIdentifier API team + + * Schedule: First Friday of each month at 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96981252767?password=fc957607-cc06-450f-b80a-229bb6a88c39) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/yjve) +* Mailing List (of DeviceIdentifier) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS.yaml b/original/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS.yaml new file mode 100644 index 0000000000000000000000000000000000000000..6aa151db705c2fac6ace419fcc9eefaa4767af4b --- /dev/null +++ b/original/DeviceAuthenticity/code/API_definitions/IMEI-FRAUD-OAS.yaml @@ -0,0 +1,518 @@ +openapi: 3.0.3 +info: + title: IMEI Fraud Check + version: wip + description: | + # Summary + + The IMEI Fraud Check API allows clients to verify the status of mobile devices using their IMEI (International Mobile Equipment Identity) across three operator-managed registers: allowed lists, prohibited lists, and tracked lists. + + This API is useful for various scenarios: + - Device registration and network access control + - Insurance claims validation - verify if a claimed lost/stolen device is actually prohibited + - Device purchase verification - check if a second-hand device has a clean status + - Fraud prevention - detect potentially fraudulent devices before service activation + - Compliance with regulatory requirements for device management + - Network monitoring and tracking of specific devices + + # Introduction + + The International Mobile Equipment Identity (IMEI) is a unique identifier assigned to mobile devices by manufacturers. This 15-digit number serves as a fingerprint for each device and is used by mobile networks to identify equipment on their networks. + + Mobile operators maintain three distinct registers for IMEI management: + + ## Register Types + + ### Allowed List (White List) + Contains all number series of equipment identities that are permitted for use on the network. Devices on this list are explicitly authorized for network access. + + ### Prohibited List (Black List) + Contains all equipment identities that belong to equipment that must be barred from network access. This includes devices that are: + - **Lost**: Device reported missing by the subscriber + - **Stolen**: Device reported stolen by the subscriber or law enforcement + - **Blacklisted**: Device blocked due to fraud, non-payment, or other policy violations + - **Blocked**: Device restricted from network access for regulatory or technical reasons + + ### Tracked List (Gray List) + Contains equipment identities that are monitored by the network for evaluation or other purposes. Devices on the tracked list are not barred from network access (unless they are also on the prohibited list or not on the allowed list), but their network activity is logged and monitored. + + The use of these registers is at the operators' discretion, and the specific implementation may vary between different network operators and jurisdictions. + + # Relevant terms and definitions + + ### IMEI Fraud Check API service endpoint + The URL pointing to the RESTful resource of the IMEI Fraud Check API. + + ### International Mobile Equipment Identity (IMEI) + A unique 15-digit identifier assigned to mobile devices by the manufacturer, used to identify the device on mobile networks. + + ### Register Status + The classification of a device based on its presence in operator-maintained registers (allowed, prohibited, tracked lists). + + ### Device Status + The operational status of a device on the network, determined by evaluating its presence across all applicable registers. + + # API functionality + + The API defines one primary service endpoint: + + - `POST /check-status` to verify the register and operational status of a device using its IMEI + + To call this endpoint, the API consumer must first obtain a valid access token from the token endpoint, which is then passed as an Authorization header. The API consumer must provide the IMEI of the device to be checked in the request body. + + If the request is valid, the API response is a JSON object containing the device status and register information: + - The response will always contain `imei` and `operationalStatus`. + - A `lastChecked` field indicates when the information was last verified + - If the device has a negative status, `reportedDate` and `prohibitedReason` may be included if available + - Other response parameters are implementation dependent + + An example of a JSON response object is as follows: + ``` + { + "lastChecked": "2024-02-20T10:41:38.657Z", + "imei": "490154203237518", + "operationalStatus": "prohibited", + "prohibitedReason": "stolen", + "reportedDate": "2023-05-23T21:48:42.000Z" + } + ``` + + ## Status Determination Logic + + The operational status is determined based on register presence: + 1. If the device is on the **prohibited list**: status is "prohibited" (regardless of other lists) + 2. If the device is on the **allowed list** and not on prohibited list: status is "allowed" + 3. If the device is only on the **tracked list**: status is "tracked" + 4. If the device is not on any list: status is "unknown" + + ## Error handling + + Errors may be returned for the following reasons. Note that this list is not exhaustive. + + `401 UNAUTHENTICATED`: + - The access token is not a valid access token for the API provider + - The access token was valid but has now expired + + `400 INVALID_ARGUMENT`: + - The API request is not compliant with this OAS definition + - Invalid IMEI format provided + + `400 OUT_OF_RANGE`: + - A parameter value in the API request is outside the documented range + + `404 IDENTIFIER_NOT_FOUND`: + - The IMEI provided in the request is not found in any accessible database + + `403 PERMISSION_DENIED`: + - The access token does not have the required scope for the endpoint being called + + `422 SERVICE_NOT_APPLICABLE`: + - The IMEI fraud check service cannot be applied to the provided identifier + + `429 QUOTA_EXCEEDED`: + - The API consumer has exceeded their allocated quota for this API + + `429 TOO_MANY_REQUESTS`: + - The rate limit for API requests has been exceeded + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 + + +servers: + - url: "{apiRoot}/imei-fraud-check/vwip" + variables: + apiRoot: + default: https://api.example.com + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: IMEI Fraud Check + description: Check the register status of mobile devices using their IMEI + +paths: + "/check-status": + post: + summary: Check the register status of a device using its IMEI + description: Verify if an IMEI is present in allowed, prohibited, or tracked lists maintained by operators + operationId: checkImeiStatus + tags: + - IMEI Fraud Check + security: + - openId: + - imei-fraud-check:check-status + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: IMEI to be checked for register status + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Check IMEI Status: + $ref: '#/components/examples/CheckImeiStatus' + + responses: + "200": + $ref: '#/components/responses/200CheckStatus' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs. The OpenID Connect discovery URL will be provided by the API provider during onboarding. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + 200CheckStatus: + description: IMEI register status has been successfully retrieved + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/ImeiStatus" + examples: + Allowed IMEI: + description: IMEI status check for an allowed device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237518" + operationalStatus: "allowed" + Prohibited IMEI (Stolen): + description: IMEI status check for a prohibited device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237519" + operationalStatus: "prohibited" + prohibitedReason: "stolen" + reportedDate: "2023-05-23T21:48:42.000Z" + Tracked IMEI: + description: IMEI status check for a tracked device + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237520" + operationalStatus: "tracked" + Unknown IMEI: + description: IMEI status check for a device not in any register + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237521" + operationalStatus: "unknown" + Multi-Register IMEI: + description: IMEI present in multiple registers (prohibited takes precedence) + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imei: "490154203237522" + operationalStatus: "prohibited" + prohibitedReason: "blacklisted" + reportedDate: "2023-08-15T14:30:22.000Z" + + 400BadRequest: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Invalid IMEI Format: + description: IMEI format is invalid + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid IMEI format. IMEI must be 15 digits." + Missing IMEI: + description: IMEI parameter is missing + value: + status: 400 + code: INVALID_ARGUMENT + message: "IMEI is required" + + 401Unauthorized: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated Request: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + 403Forbidden: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permission Denied: + description: Access token does not have required scope + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + 404NotFound: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + IMEI Not Found: + description: The provided IMEI is not found in any database + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The provided IMEI cannot be found in any accessible database. + + 422UnprocessableContent: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + Service Not Applicable: + description: The fraud check service is not applicable for this IMEI + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The fraud check service is not applicable for the provided IMEI. + + 429TooManyRequests: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + Too Many Requests: + description: Rate limit exceeded + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached + Quota Exceeded: + description: API quota exceeded + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota + + schemas: + CommonResponseBody: + description: Common parameters included in all responses + properties: + lastChecked: + description: | + Date and time that the information was last confirmed by the fraud check service to be correct. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ImeiStatus: + description: The register and operational status information for the queried IMEI + type: object + properties: + imei: + type: string + description: The IMEI that was checked + pattern: '^[0-9]{15}$' + example: "490154203237518" + operationalStatus: + type: string + description: The operational status of the device, determined by register presence + enum: + - allowed + - prohibited + - tracked + - unknown + example: "allowed" + prohibitedReason: + type: string + description: Reason why the IMEI is prohibited. Only included when operationalStatus is "prohibited". + enum: + - lost + - stolen + - blacklisted + - blocked + - fraud + - non-payment + - regulatory + example: "stolen" + reportedDate: + type: string + format: date-time + description: | + Date and time when the IMEI was reported with its current prohibited status (only present when operationalStatus is "prohibited"). It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-05-23T21:48:42.000Z" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the error represents + + RequestBody: + description: Request body for IMEI register status check + type: object + required: + - imei + properties: + imei: + type: string + description: The IMEI number of the device to check (15 digits) + pattern: '^[0-9]{15}$' + example: "490154203237518" + + XCorrelator: + type: string + pattern: '^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$' + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + examples: + CheckImeiStatus: + description: Example request to check IMEI register status + value: + imei: "490154203237518" diff --git a/original/DeviceAuthenticity/code/API_definitions/README.MD b/original/DeviceAuthenticity/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/DeviceAuthenticity/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/DeviceAuthenticity/documentation/API_documentation/README.MD b/original/DeviceAuthenticity/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceAuthenticity/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceAuthenticity/documentation/SupportingDocuments/README.MD b/original/DeviceAuthenticity/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceAuthenticity/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceDataVolume/README.md b/original/DeviceDataVolume/README.md new file mode 100644 index 0000000000000000000000000000000000000000..c7f1e49b4da584db3db763e126a793c4dec1ec42 --- /dev/null +++ b/original/DeviceDataVolume/README.md @@ -0,0 +1,56 @@ + + + + + + + + + +# DeviceDataVolume + +Sandbox API Repository to describe, develop, document, and test the DeviceDataVolume APIs within the Sub Project [DeviceStatus](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/PoCaBQ) + +## Scope + +* Service APIs “Device Data Volume” and "Device Data Volume Subscriptions" (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The service APIs provide the customer with the ability to: + * get detailed insights into the customer's data usage status + * get alerts when the customer's data usage status changes +* Describe, develop, document, and test the service APIs +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/DeviceDataVolume/releases/tag/r1.3) (Fall25), with the following API versions: + * **device-data-volume-subscriptions v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceDataVolume/blob/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume-subscriptions.yaml) + * **device-data-volume v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceDataVolume/blob/r1.3/code/API_definitions/device-data-volume.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceDataVolume/r1.3/code/API_definitions/device-data-volume.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceDataVolume/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceDataVolume/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceDataVolume/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings for the DeviceStatus Sub Project are held virtually + * Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions.yaml b/original/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..9e8f78d77e948759800651ed2b245a1c9820160c --- /dev/null +++ b/original/DeviceDataVolume/code/API_definitions/device-data-volume-subscriptions.yaml @@ -0,0 +1,1711 @@ +openapi: 3.0.3 +info: + title: Device Data Volume Subscriptions + description: | + This API enables customers to subscribe to events related to data volume usage thresholds on a device. It supports both request and subscription modes to track remaining data volume. + + # Introduction + + ## Device Data Volume Subscriptions + + API consumers can receive notifications regarding data volume usage thresholds, such as when the remaining data volume reaches 50%, 75%, or 90% of the user's allocated data plan. This is useful for managing data usage and avoiding overage fees. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity capable of network communication, identified via an IP address, phone number, or Network Access Identifier. + + # API Functionality + + The API exposes the following capabilities: + + ## Device Data Volume Subscriptions + + These endpoints allow management of subscriptions to data volume usage events. The CAMARA subscription model follows the CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` related to data volume thresholds you wish to track. + + The following event `types` are managed for this API: + - `org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent`: Event triggered when 50% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent`: Event triggered when 75% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent`: Event triggered when 90% of the data plan is consumed. + - `org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded`: Event triggered when the data plan is exceeded. + + Note: Additionally, the following events could be send, which do not require a dedicated subscription: + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding device data volume events can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceDataVolume + +servers: + - url: "{apiRoot}/device-data-volume-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Device Data Volume Subscriptions + description: Manage subscriptions to device data volume usage events. + +paths: + /subscriptions: + post: + tags: + - Device data volume subscription + summary: "Create a device data volume event subscription" + description: Create a subscription for data volume usage events + operationId: createDeviceDataVolumeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent:create + - device-data-volume-subscriptions:org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Data Volume server will call this endpoint whenever a data volume usage event occurs. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + data-50-percent: + $ref: "#/components/examples/DATA_50_PERCENT" + data-75-percent: + $ref: "#/components/examples/DATA_75_PERCENT" + data-90-percent: + $ref: "#/components/examples/DATA_90_PERCENT" + data-exceeded: + $ref: "#/components/examples/DATA_EXCEEDED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Successful Subscription Creation: + $ref: "#/components/examples/SUBSCRIPTION_CREATION" + Successful Subscription Creation With Device Disambiguation: + $ref: "#/components/examples/SUBSCRIPTION_CREATION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Device data volume subscription + summary: "Retrieve a list of device data volume subscriptions" + description: Retrieve a list of data volume usage event subscription(s) + operationId: retrieveDeviceDataVolumeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-data-volume-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + examples: + Subscription List: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty Subscription List: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device data volume subscription + summary: "Retrieve a device data volume event subscription" + description: Retrieve a specific subscription by ID + operationId: retrieveDeviceDataVolumeSubscription + security: + - openId: + - device-data-volume-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device data volume subscription + summary: "Delete a device data volume event subscription" + operationId: deleteDeviceDataVolumeSubscription + description: | + This operation deletes a specific data volume usage subscription by its subscription ID. + Once deleted, no more notifications will be sent for the corresponding subscription. + security: + - openId: + - device-data-volume-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: No Content - Subscription successfully deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now. + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential for authentication, containing an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier (e.g., username). + type: string + secret: + description: The secret (e.g., password). + type: string + + AccessTokenCredential: + type: object + description: An access token credential for authentication. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: A previously acquired token for accessing the resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: Expiry time for the access token. + accessTokenType: + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetail: + description: The details of the requested device data volume subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + Subscription: + description: Represents a device data volume subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address where events will be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription for device data volume. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + id: + $ref: "#/components/schemas/SubscriptionId" + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionEventType: + type: string + description: | + Event types that can be triggered for device data volume monitoring. + enum: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + format: uuid + description: Unique identifier for the subscription. + example: 550e8400-e29b-41d4-a716-446655440000 + + NotificationEventType: + type: string + description: | + data-50-percent - Event triggered when the device reaches 50% data usage thresholds of the data plan used. + + data-75-percent - Event triggered when the device reaches 75% data usage thresholds of the data plan used. + + data-90-percent - Event triggered when the device reaches 90% data usage thresholds of the data plan used. + + data-exceeded - Event triggered when the device reaches 100% data usage exceeded of the data plan used. + + subscription-started: Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription is terminated. + enum: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + - org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-started + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated + - org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + - data + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + example: sd5e-uy52-88t4-za66 + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/NotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent: "#/components/schemas/EventDataUsage50Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent: "#/components/schemas/EventDataUsage75Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent: "#/components/schemas/EventDataUsage90Percent" + org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded: "#/components/schemas/EventDataUsageExceeded" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have a time zone. + example: "2018-04-05T17:31:00Z" + + # Event structures for data volume + EventDataUsage50Percent: + description: Event structure for data usage 50% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsage75Percent: + description: Event structure for data usage 75% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsage90Percent: + description: Event structure for data usage 90% threshold alerts + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventDataUsageExceeded: + description: Event structure for data usage exceeding the allocated volume + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: Event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: | + Event detail structure for org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended event. + Note that the device object is defined as optional and will only to be returned if provided in createSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createSubscription). + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_UNPROCESSABLE - Subscription cannot be processed due to some reason. Useful for asynchronous subscription creation. + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_UNPROCESSABLE + - SUBSCRIPTION_EXPIRED + - SUBSCRIPTION_DELETED + - ACCESS_TOKEN_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: SUBSCRIPTION_MISMATCH + message: Inconsistent access token for requested events subscription + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ALREADY_EXISTS + examples: + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + DATA_50_PERCENT: + value: + id: "124007" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1406" + time: "2024-05-12T12:45:23.682Z" + + DATA_75_PERCENT: + value: + id: "124008" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-75-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1407" + time: "2024-05-12T14:30:23.682Z" + + DATA_90_PERCENT: + value: + id: "124009" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-90-percent + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1408" + time: "2024-05-12T16:15:23.682Z" + + DATA_EXCEEDED: + value: + id: "124010" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: "dv10-h556-rt89-1409" + time: "2024-05-12T18:00:23.682Z" + + SUBSCRIPTION_STARTED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ENDED: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.device-data-volume-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_CREATION: + description: A new subscription has been successfully created + value: + protocol: HTTP + protocolSettings: + method: POST + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + config: + subscriptionDetail: {} + subscriptionExpireTime: '2023-01-17T13:18:23.682Z' + subscriptionMaxEvents: 5 + initialEvent: true + id: 550e8400-e29b-41d4-a716-446655440000 + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + SUBSCRIPTION_CREATION_WITH_DEVICE_DISAMBIGUATION: + description: A new subscription has been successfully created + value: + protocol: HTTP + protocolSettings: + method: POST + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.device-data-volume-subscriptions.v0.data-50-percent + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: '2023-01-17T13:18:23.682Z' + subscriptionMaxEvents: 5 + initialEvent: true + id: 550e8400-e29b-41d4-a716-446655440000 + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + ACTIVE_SUBSCRIPTION: + description: Details of an active subscription + value: + id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + description: Details of an active subscription with device details for disambiguation + value: + id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440001 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-data-volume-subscriptions.v0.data-exceeded" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-08-01T14:18:23.682Z" + subscriptionMaxEvents: 10 + initialEvent: true + status: ACTIVE + startsAt: '2023-01-17T12:27:08.312Z' + expiresAt: '2023-01-17T13:18:23.682Z' + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] diff --git a/original/DeviceDataVolume/code/API_definitions/device-data-volume.yaml b/original/DeviceDataVolume/code/API_definitions/device-data-volume.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fb488e1dfc978e5f780fefac06ff4e624968bfed --- /dev/null +++ b/original/DeviceDataVolume/code/API_definitions/device-data-volume.yaml @@ -0,0 +1,550 @@ +openapi: 3.0.3 +info: + title: Device Data Volume + description: | + This API offers detailed insights into the customer's data usage status, including available data volume and their current position within the volume allocation. + + # Introduction + + API consumers are able to retrieve data usage information for a dedicated SIM card, offering estimated remaining data volume categories like <200MiB, <1GiB, <5GiB, and >=5GiB. It also allows subscription to changes in data volume status. + + Additionally, a check operation is provided to determine if the remaining data volume exceeds a user-specified threshold. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes two endpoints/operations: + + - The endpoint `POST /retrieve` allows customers to retrieve the remaining device data volume. + - The endpoint `POST /check` allows customers to check if the remaining data volume is above a certain threshold. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceDataVolume + +servers: + - url: "{apiRoot}/device-data-volume/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Device Data Volume + description: Operations related to remaining device data volume of a user device + +paths: + /retrieve: + post: + tags: + - Device Data Volume + summary: "Execute device data volume retrieval for a user device" + description: Retrieve the estimated remaining data volume for a device. + operationId: retrieveDataVolume + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-data-volume:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveDataVolumeRequest" + required: true + responses: + "200": + description: Contains information about the remaining device data volume. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveDataVolumeResponse" + examples: + Successful Response: + $ref: "#/components/examples/SuccessfulRetrieveResponse" + Successful Response With Device Disambiguation: + $ref: "#/components/examples/SuccessfulRetrieveResponseWithDeviceDisambiguation" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + + /check: + post: + tags: + - Device Data Volume + summary: "Check if the remaining data volume is above a certain threshold" + description: Check if the remaining data volume for a device is above a given threshold. + operationId: checkDataVolume + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-data-volume:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDataVolumeRequest" + required: true + responses: + "200": + description: Boolean response indicating if the remaining data volume exceeds the provided threshold + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDataVolumeResponse" + examples: + Successful Response: + $ref: "#/components/examples/SuccessfulCheckResponse" + Successful Response With Device Disambiguation: + $ref: "#/components/examples/SuccessfulCheckResponseWithDeviceDisambiguation" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + description: Correlation id for the different services + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + CheckDataVolumeRequest: + description: | + The request to check, if the current remaining data volume is above the requested threshold. + Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + volumeToCheck: + type: object + description: Volume threshold to check against + properties: + value: + description: Quantity of volume to check + type: integer + example: 500 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/VolumeUnitEnum" + required: + - value + - unit + required: + - volumeToCheck + + VolumeUnitEnum: + description: Enumeration of volume units, where "MiB" is 2^20 bytes and "GiB" is 2^30 bytes. + type: string + enum: + - MiB + - GiB + + CheckDataVolumeResponse: + description: Represents the response, if the data volume exceeds a given threshold. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + thresholdExceeded: + type: boolean + description: Indicates whether the remaining data volume exceeds the given threshold + required: + - thresholdExceeded + + RetrieveDataVolumeRequest: + description: | + The request to retrieve the current remaining data volume for the requested device. + Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveDataVolumeResponse: + description: Represents the remaining data volume of the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + dataVolumeCategory: + $ref: "#/components/schemas/DataVolumeCategory" + required: + - dataVolumeCategory + + DataVolumeCategory: + description: Estimated remaining data volume category, where "MiB" is 2^20 bytes and "GiB" is 2^30 bytes. + type: string + enum: + - "<200MiB" + - "<1GiB" + - "<5GiB" + - ">=5GiB" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + summary: Missing identifier + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + summary: Unnecessary identifier + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + + examples: + SuccessfulRetrieveResponse: + description: Successfully retrieve the device data volume category + value: + dataVolumeCategory: "<200MiB" + SuccessfulRetrieveResponseWithDeviceDisambiguation: + description: Successfully retrieve the device data volume category but device disambiguation is required + value: + device: + phoneNumber: "+123456789" + dataVolumeCategory: "<200MiB" + SuccessfulCheckResponse: + description: Successfully check the device data volume category + value: + thresholdExceeded: false + SuccessfulCheckResponseWithDeviceDisambiguation: + description: Successfully check the device data volume category but device disambiguation is required + value: + device: + phoneNumber: "+123456789" + thresholdExceeded: true diff --git a/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist.md b/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..0d876394180017644108d69af1fd81e9d95d1ac5 --- /dev/null +++ b/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for device-data-volume v0.1.0 in r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-----------------:|:-----------------:|:------:|:---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-data-volume.yaml](/code/API_definitions/device-data-volume.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [checkDataVolume.feature](/code/Test_definitions/device-data-volume-checkDataVolume.feature)
                                                          [retrieveDataVolume.feature](/code/Test_definitions/device-data-volume-retrieveDataVolume.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [checkDataVolume.feature](/code/Test_definitions/device-data-volume-checkDataVolume.feature)
                                                          [retrieveDataVolume.feature](/code/Test_definitions/device-data-volume-retrieveDataVolume.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/wYFmBQ) | diff --git a/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist.md b/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..7223da9ad485b8e0a22fe30e56a8e867eb713cfc --- /dev/null +++ b/original/DeviceDataVolume/documentation/API_documentation/device-data-volume-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for device-data-volume-subscriptions v0.1.0 in r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                          public | stable
                                                          public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-----------------:|:-----------------:|:------:|:----------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-data-volume-subscriptions.yaml](/code/API_definitions/device-data-volume-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [subscriptions.feature](/code/Test_definitions/device-data-volume-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [subscriptions.feature](/code/Test_definitions/device-data-volume-subscriptions.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/PIPFBQ) | diff --git a/original/DeviceDataVolume/documentation/SupportingDocuments/README.MD b/original/DeviceDataVolume/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceDataVolume/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceIdentifier/README.md b/original/DeviceIdentifier/README.md new file mode 100644 index 0000000000000000000000000000000000000000..7a7a36de6839dc147f9e97dc4b568700f6a93833 --- /dev/null +++ b/original/DeviceIdentifier/README.md @@ -0,0 +1,52 @@ + + + + + + + + + +# DeviceIdentifier + +Sandbox API Repository to describe, develop, document, and test the DeviceIdentifier Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/czLe) + +## Scope + +* Service API “DeviceIdentifier” (see [APIBacklog](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API consumer with the ability to: + * Retrieve the current identity (IMEI) of the mobile device being used by a given mobile subscriber + * Retrieve the type (manufacturer and model) of the mobile device being used by a given mobile subscriber +* Describe, develop, document, and test the API +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/DeviceIdentifier/releases/tag/r2.2) (Fall25), with the following API versions: + * **device-identifier v0.3.0** + [[YAML]](https://github.com/camaraproject/DeviceIdentifier/blob/r2.2/code/API_definitions/device-identifier.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/r2.2/code/API_definitions/device-identifier.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/r2.2/code/API_definitions/device-identifier.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceIdentifier/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceIdentifier/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceIdentifier/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: First Friday of each month at 15:00 UTC via Linux Foundation Zoom service + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96981252767?password=fc957607-cc06-450f-b80a-229bb6a88c39) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564298/DeviceIdentifier+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list [https://lists.camaraproject.org/g/sp-dvi](https://lists.camaraproject.org/g/sp-dvi) . + * A message to the community of this Sub Project can be sent using [sp-dvi@lists.camaraproject.org](mailto:sp-dvi@lists.camaraproject.org). diff --git a/original/DeviceIdentifier/code/API_definitions/device-identifier.yaml b/original/DeviceIdentifier/code/API_definitions/device-identifier.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e1500227c918f641ada93ae9f08309de9bf4a906 --- /dev/null +++ b/original/DeviceIdentifier/code/API_definitions/device-identifier.yaml @@ -0,0 +1,865 @@ +openapi: 3.0.3 +info: + title: Device Identifier + version: wip + description: | + # Summary + + The Mobile Device Identifier API returns details of the physical mobile device currently being used by a specified mobile subscriber. The following information can be returned: + - A unique network identifier for the specific device itself (IMEI SV and IMEI) + - A pseudonymised network identifier for the specific device itself (Pairwise Pseudonymous Identifier) + - A network identifier for the device make and model (IMEI Type Allocation Code) + - Device manufacturer name and model + + This information can be useful in a number of scenarios, such as the following: + - For insurance purposes, to automatically identify a device that a customer wishes to insure + - For security / fraud reasons, to establish that a customer is not using a device they claim to have broken or lost + - For service delivery reasons, to optimise content for a particular device or OS type + + # Introduction + + Mobile devices are allocated a unique identifier by the manufacturer, known as the International Mobile Equipment Identity, or IMEI. The current software version (SV) of the device can be appended to this, in which case the identifier is known as the IMEI SV. This identifier is signalled to the mobile network when the device connects, both to confirm that the device is not blocked, and also allow device dependent network configurations to be implemented. + + The IMEI is a 15 digit integer, and the IMEI SV is a 16 digit integer: + - The first 8 digits are known as the Type Allocation Code (TAC), and identify the manufacturer and model of the device + - The following 6 digits are the serial number of the device for that TAC + - For IMEI, the remaining digit is a check digit + - For IMEI SV, the remaining two digits are the software version + + TACs are issued and managed by the GSMA, and can be queried using the [GSMA IMEI database](https://www.gsma.com/aboutus/workinggroups/terminal-steering-group/imei-database). + + The mobile network associates this device identifier with the mobile subscription currently using the device. The mobile subscription is defined by the Subscriber Identity Module (SIM) currently active in the mobile device. This may be a removable SIM or an eSIM. In either case, it is possible for the association between the device identifier and subscription to change - for example, when a physical SIM is transferred to another mobile device. + + ![Device Identifier API Overview](https://raw.githubusercontent.com/camaraproject/DeviceIdentifier/main/documentation/API_documentation/resources/Device_Identifier_Overview.png) + + The Device Identifier API allows the API consumer to obtain the IMEI and associated parameters for a specified mobile subscription identifier or equivalent. The mobile subscription can be identified using one or more of the following subscription identifiers: + - the subscription phone number (also known as MSISDN) + - the subscription network access identifier, which is a domain specific identifier typically allocated to devices that do not require voice / SMS connectivity + - the current IP address and port alloacted to the device, which must be an IPv6 or public IPv4 address + + The API can be called by an API consumer to establish an identifier for the physical device currently being used by the mobile subscription. The information returned will depend upon the consent that the end user (i.e. mobile subscription owner) has given for that information to be provided to the API consumer. For example, if the end user has not consented to any information about their device being given, then the API consumer will receive an error in response to their request. Otherwise, the information that the end user has consented to being given will be returned. + + # Relevant terms and definitions + + ### Device Identifier API service endpoint + The URL pointing to the RESTful resource of the Device Identifier API. + + ### Identifier for the mobile subscription + At least one identifier for the mobile subscription from the following four options: + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + ### Identifier for the physical mobile device + The IMEI or IMEISV of the physical mobile device + + ### Pairwise Pseudonymous Identifier + An identifier that has been pseudonymised such that the resulting pseudonymous identifier is unique to but persistent for a given API consumer + + # API functionality + + The API defines three service endpoints: + + - `POST /retrieve-identifier` to get details about the specific device being used by a given mobile subscriber, including IMEI / IMEISV and the type of device + - `POST /retrieve-type` to get details only about the type (i.e. manufacturer and model) of device being used by a given mobile subscriber + - `POST /retrieve-ppid` to get a pseudonymised identifier for the specific device being used by a given mobile subscriber + + To call any of these endpoints, the API consumer must first obtain a valid access token from the token endpoint, which is then passed as an Authorization header. When a 2-legged access token is used, the API consumer must also pass at least one of the available mobile subscription identifiers in the body of the request. + + If the request is valid, the API response is a JSON object containing the data that the end user has consented to sharing with the API consumer. + - When calling endpoint `retrieve-identifier`, the response will always contain `imei` + - When calling endpoint `retrieve-type`, the response will always contain `tac` + - When calling endpoint `retrieve-ppid`, the response will always contain `ppid` + - Responses will also always contain a `lastChecked` field, indicating when the information provided was last confirmed to be correct + - Other response parameters are implementation dependent, and thus optional + + An example of a JSON response object is as follows: + ``` + { + "lastChecked": "2024-02-20T10:41:38.657Z", + "imeisv": "49015420323751800", + "imei": "4901542032375181", + "tac": "49015420", + "model": "3110", + "manufacturer": "Nokia" + } + ``` + + ## Error handling + + Errors may be returned for the following reasons. Note that this list is not exhaustive. + + `401 UNAUTHENTICATED`: + - The access token is not a valid access token for the API provider + - The access token was valid but has now expired + + `400 INVALID_ARGUMENT`: + - The API request is not compliant with this OAS definition + + `400 OUT_OF_RANGE`: + - A parameter value in the API request is outwith the range documented in this OAS definition for that parameter + + `404 IDENTIFIER_NOT_FOUND`: + - The device identified by the `device` object in the request is not managed by the API provider + + `403 PERMISSION_DENIED`: + - The access token does not have the required scope for the endpoint being called + - The end user has not consented to the API consumer getting access to the device identifier information (2-legged access token only) + + `422 SERVICE_NOT_APPLICABLE`: + - A device identifier cannot be provided for the identified device. For example, the phone number might identify a landline. + + `422 UNSUPPORTED_IDENTIFIER`: + - A parameter provided in the `device` object is not supported by this implementation (e.g. `networkAccessIdentifier`) + + `422 MISSING_IDENTIFIER`: + `422 UNNECESSARY_IDENTIFIER`: + - See the section "Identifying the device from the access token" below + + `429 QUOTA_EXCEEDED`: + - The API consumer has used up the quota of API requests that they were allocated for this API + + `429 TOO_MANY_REQUESTS`: + - The rate at which the API consumer is sending requests has exceeded that allowed by the API provider. Try again later. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In scenarios where a main phone number is shared between multiple devices, each of which has its own individual "secondary" phone number (e.g. connectivity plans that let you share your airtime and data allowances with a smartwatch or eSIM-enabled tablet), the phone number passed by the API consumer will be treated as the secondary phone number, and hence the identifier returned will be that of the single device associated with that phone number (e.g. smartphone, smartwatch, or eSIM-enabled tablet). + + In such scenarios, the "primary" device is usually allocated the same main and secondary phone numbers, and hence providing the main phone number to the API will return the identity of the primary device (usually the smartphone) and not any associated devices. + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceIdentifier + +servers: + - url: "{apiRoot}/device-identifier/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Get Device Identifiers + description: Retrieve details about the device being used by a mobile subscriber + +paths: + "/retrieve-identifier": + post: + summary: Get details about the specific device being used by a given mobile subscriber + description: Get details about the specific device being used by a given mobile subscriber + operationId: retrieveIdentifier + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-identifier + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrieveIdentifier' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + + "/retrieve-type": + post: + summary: Get details about the type of device being used by a given mobile subscriber + description: Get details about the type of device being used by a given mobile subscriber + operationId: retrieveType + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-type + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrieveType' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + + "/retrieve-ppid": + post: + summary: Get a pseudonymous identifier for device being used by a given mobile subscriber + description: Get a pseudonymous identifier for device being used by a given mobile subscriber + operationId: retrievePPID + tags: + - Get Device Identifiers + security: + - openId: + - device-identifier:retrieve-ppid + parameters: + - $ref: "#/components/parameters/x-correlator" + + requestBody: + description: Parameters to identify the mobile subscription when a 2-legged access token is being used + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: '#/components/responses/200RetrievePPID' + "400": + $ref: '#/components/responses/400BadRequest' + "401": + $ref: '#/components/responses/401Unauthorized' + "403": + $ref: '#/components/responses/403Forbidden' + "404": + $ref: '#/components/responses/404NotFound' + "422": + $ref: '#/components/responses/422UnprocessableContent' + "429": + $ref: '#/components/responses/429TooManyRequests' + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + 200RetrieveIdentifier: + description: An device identifier has been found for the specified subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - imei + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DeviceIdentifier" + - $ref: "#/components/schemas/DeviceType" + examples: + Successful Identifier Retrieval: + description: Device identifier has been successfully retrieved when the device subscription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + imeisv: "49015420323751800" + imei: "4901542032375181" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + Successful Identifier Retrieval With Device Disambiguation: + description: Device identifier has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + imeisv: "49015420323751800" + imei: "4901542032375181" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + + 200RetrieveType: + description: A device identifier has been found for the specified subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - tac + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DeviceType" + examples: + Successful Type Retrieval: + description: Device type has been successfully retrieved when the device subcsription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + Successful Type Retrieval With Device Disambiguation: + description: Device type has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + tac: "49015420" + model: "3110" + manufacturer: "Nokia" + + 200RetrievePPID: + description: A pseudonymous device identifier has been found for the specified mobile subscriber + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + required: + - lastChecked + - ppid + allOf: + - $ref: "#/components/schemas/CommonResponseBody" + - $ref: "#/components/schemas/DevicePPID" + examples: + Successful PPID Retrieval: + description: Device PPID has been successfully retrieved when the device subcsription was identified by a 3-legged access token or single device subscription identifier + value: + lastChecked: "2024-02-20T10:41:38.657Z" + ppid: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + Successful PPID Retrieval With Device Disambiguation: + description: Device PPID has been successfully retrieved when a 2-legged access token and multiple device subscription identifiers were provided + value: + device: + phoneNumber: "+123456789" + lastChecked: "2024-02-20T10:41:38.657Z" + ppid: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + + 400BadRequest: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: OUT_OF_RANGE + message: "Invalid value: ipv4Address.publicPort" + + 401Unauthorized: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated Request: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + 403Forbidden: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permision Denied: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + 404NotFound: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + Device Cannot Be Found: + description: The provided identifier cannot be matched to a device known to the API provider + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The provided identifier cannot be matched to a device. + + 422UnprocessableContent: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Service Not Applicable For Device: + description: The service is not applicable for the identified device + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the identified device. + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + + 429TooManyRequests: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + Too Many Requests: + description: Access to the API has been temporarily blocked due to quota or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached + Quota Exceeded: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota + + schemas: + CommonResponseBody: + description: | + Common parameters to be included in all responses + properties: + device: + description: The device subscription identifier that was used to identify the device whose identifier is being returned. If this property is not present, then the device subscription identifier specified in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + lastChecked: + description: | + Date and time that the information was last confirmed by the mobile operator to be correct. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + DeviceIdentifier: + description: | + The individual physical mobile device identifier, as expressed by the IMEI and IMEISV + type: object + properties: + imeisv: + type: string + description: IMEISV of the device + example: "49015420323751800" + imei: + type: string + description: IMEI of the device + example: "4901542032375181" + + DeviceType: + description: | + The physical device type, as expressed by Type Approval Code, manufacturer name and model name + type: object + properties: + tac: + type: string + description: IMEI TAC of the device + example: "49015420" + model: + type: string + description: Model of the device + example: "3110" + manufacturer: + type: string + description: Manufacturer of the device + example: "Nokia" + + DevicePPID: + description: | + The individual physical mobile device identifier, expressed as a PPID (Pairwise Pseudonymous Identifier) + type: object + properties: + ppid: + type: string + description: A PPID for the identified physical device + example: "b083f65ccdad365d7489fff24b6d5074b30c12b6d81db3404d25964ffd908813" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE 1: The MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + NOTE 2: For the current Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "84.125.93.10", + "publicPort": 59765 + } + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + RequestBody: + description: Common request body to allow optional Device object to be passed + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + {} + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@example.com" diff --git a/original/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story.md b/original/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..6aa86f0d55984387d841af11d92d031b41ef028c --- /dev/null +++ b/original/DeviceIdentifier/documentation/API_documentation/Device_Identifier_User_Story.md @@ -0,0 +1,44 @@ +# Device Identifier API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want my application server to be able to request the identity of the mobile device (represented by the IMEI) currently being used by a given mobile network subscriber (identified by MSISDN, IP address or, when supported by network operators, a Network Access Identifier). Optionally, I'd like to know the make and model of that device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                          **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
                                                          **Scope:** *Order To Activate (OTA)* \- Retrieve device identifier details | +| ***Pre-Conditions*** |The preconditions are listed below:
                                                          1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                          2. The Customer:BusinessManager has successfully subscribed to the Device Identifier product from the product catalog.
                                                          3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                          4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
                                                          5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User's application server makes a POST request to the Device Identifier API containing the end user's subscription information in the request body in order to retrieve the device identifier plus any optional device information.
                                                            **Ends when:** The Device Identifier API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Identifier API
                                                            - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                                                            - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                                            - **Forbidden**: End user has not consented to device identifier information being provided to the Customer:User| + +# EUDI Wallet Device-Binding User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer working for an EUDI Wallet provider, I want to bind the user's wallet to their device. For that purpose I want to retrieve the device identifier of the user's device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                            **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
                                                            **Scope:** *Order To Activate (OTA)* \- Retrieve device identifier details | +| ***Pre-Conditions*** |The preconditions are listed below:
                                                            1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                            2. The Customer:BusinessManager has successfully subscribed to the Device Identifier product from the product catalog.
                                                            3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                            4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
                                                            5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User has installed the EUDI Wallet and the wallet runs for the first time. The EUDI Wallet retrieves an access-token using OIDC authentication code flow and creates a POST request to the DeviceIdentifier API to retrieve the device identifer.
                                                              **Ends when:** The Device Identifier API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Identifier API
                                                              - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                                                              - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                                              - **Forbidden**: End user has not consented to device identifier information being provided to the Customer:User| + +# Device Type API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want my application server to be able to request details about the type of the mobile device (represented by the Type Approval Code - TAC) currently being used by a given mobile network subscriber (identified by MSISDN, IP address or, when supported by network operators, a Network Access Identifier). Optionally, I'd like to know the make and model of that device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                              **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
                                                              **Scope:** *Order To Activate (OTA)* \- Retrieve device type details | +| ***Pre-Conditions*** |The preconditions are listed below:
                                                              1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                              2. The Customer:BusinessManager has successfully subscribed to the Device Type product from the product catalog.
                                                              3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                              4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
                                                              5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:User's application server makes a POST request to the Device Type API containing the end user's subscription information in the request body in order to retrieve the device TAC plus any optional device information.
                                                                **Ends when:** The Device Type API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Type API
                                                                - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                                                                - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                                                - **Forbidden**: End user has not consented to device TAC information being provided to the Customer:User| + +# Mobile Device Insurance User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer working for an insurance company that insures mobile devices, I want to retrieve the device identifier and the model and make of the user's device. The retrieved information is used in creating the contract between the insurance company and the user, and also when the user reports the device to be e.g. damaged or stolen. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                **Actors:** Application Service Providers, Hyperscalers, Application Developers, End Users
                                                                **Scope:** *Order To Activate (OTA)* \- Retrieve device type details | +| ***Pre-Conditions*** |The preconditions are listed below:
                                                                1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                                2. The Customer:BusinessManager has successfully subscribed to the Device Type product from the product catalog.
                                                                3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                                4. The Customer:BusinessManager has agreed to the terms and conditions of the CSP for managing consent of mobile subscription owners.
                                                                5. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The Customer:Applicatoin requests an access token using OIDC authorization code flow and then uses the DeviceIdentifier API to retrieve device identifier and model and make of the user's devive.
                                                                  **Ends when:** The Device Type API returns the requested information, or an error message | +| ***Post-Conditions*** | None | +| ***Exceptions*** | Several exceptions might occur after a request to the Device Type API
                                                                  - **Unauthorized**: Invalid credentials (e.g. use of already expired access token).
                                                                  - **Invalid Input**: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                                                  - **Forbidden**: End user has not consented to device TAC information being provided to the Customer:User| + diff --git a/original/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist.md b/original/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..e484b57514c3b3f86504f9c8b841aea4ad5b89af --- /dev/null +++ b/original/DeviceIdentifier/documentation/API_documentation/device-identifier-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for device-identifier v0.3.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                  public | stable
                                                                  public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [device-identifier.yaml](/code/API_definitions/device-identifier.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [Device Identifier User Story.md](/documentation/API_documentation/Device%20Identifier%20User%20Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-identifier-retrieveIdentifier.feature](/code/Test_definitions/device-identifier-retrieveIdentifier.feature)
                                                                  [device-identifier-retrieveType.feature](/code/Test_definitions/device-identifier-retrieveType.feature)
                                                                  [device-identifier-retrievePPID.feature](/code/Test_definitions/device-identifier-retrievePPID.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/goHWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09.md new file mode 100644 index 0000000000000000000000000000000000000000..1c7d3cf2c81f15721a23a7731a7fe65a5567d78e --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2022-12-09.md @@ -0,0 +1,12 @@ +# Meeting Minutes: Device Identifier WG +## Date: 9th December 2022 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- None +## Issues +- None +## Discussions +- None +## AOB +- No meeting on 23rd December 2022. Next meeting will be 6th January 2023. diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06.md new file mode 100644 index 0000000000000000000000000000000000000000..166690e3075b2f527044385e3024d5e8e57f07f8 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-06.md @@ -0,0 +1,21 @@ +# Meeting Minutes: Device Identifier WG +## Date: 6th January 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- None +## Issues +- None +## Discussions +### API Definition +- Eric presented an overview of the current [API definition](https://github.com/camaraproject/DeviceIdentifier/blob/main/code/API_definitions/CAMARA%20Device%20Identifier%20API.yaml). The following points were clarified: + - A `GET` call is used by this API as it is directly retrieving information from the network and not creating any sort of resource or subscription + - The agreed set of parameters used to identify a UE for all APIs (i.e. External Identifier, MSISDN and/or IP address) are used here, but passed as headers as these parameters are clearly sensitive and there is no request body to put them in. These parameters will evolve when discussions within the Commonalities WG on UE identification and user consent are concluded. + - The API can return up to 5 parameters related to the device being used by the identified UE (imei, imeisv, tac, manufacturer and model). None of these parameters is mandatory as it is an open question as to how user consent will affect the parameters that can be returned. It may be that the end user can grant or withhold consent individually for each parameter (even though some parameters can be derived from others). This issue will be revisited once the user consent process is finalised. + - Should response headers be standardised across all APIs? Or should there be a "default" set, with only additional headers listed? This is related to the API design guidelines. **Eric to open an issue in the Commonalities WG to discuss.** +### API Documentation +- API documentation will be generated once the above issue on response parameters is resolved. +## AOB +- Next meeting Friday 20th January @ 15:00 GMT diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20.md new file mode 100644 index 0000000000000000000000000000000000000000..0d66015ecc7632ce62a81f06b7f2f1b3575061cd --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-01-20.md @@ -0,0 +1,18 @@ +# Meeting Minutes: Device Identifier WG +## Date: 20th January 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- [PR #7](https://github.com/camaraproject/DeviceIdentifier/pull/7) + This is an update to the API specification to remove non-essential headers (currently being discussed in [Commonalities Issue #124](https://github.com/camaraproject/WorkingGroups/issues/124)) and extend error responses to multiple examples using `examples` rather than a single `example`. No comments raised, so will merge this PR next week. +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4): Update commonalities glossary with subproject relevant terms** + - Request from Shilpa to add WG specific terminology to the glossary. Primarily the responsibility of the WG lead, but anybody can contribute. +## Discussions +### WG Code Owners +- Current code owners are both from Vodafone. It would be useful to have additional code owners from other companies. + - **Currently neither Ludovic nor Rafal can commit to this** +## AOB +- Next meeting Friday 3rd February @ 15:00 GMT diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03.md new file mode 100644 index 0000000000000000000000000000000000000000..fc9b7522c1849147cc9033a4c9a5e552b0ae7361 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-03.md @@ -0,0 +1,16 @@ +# Meeting Minutes: Device Identifier WG +## Date: 3rd February 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- None outstanding +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4): Update commonalities glossary with subproject relevant terms** + - Still outstanding. +## Discussions +### API Evolution +- V0.0.1 of the API has now been merged into the main branch. Further evolution of the API will depend on ongoing discussions within the Commonalities WG, particularly around the design guidelines and common API definitions. No further updates will be proposed until these issues are finalised. +## AOB +- Next meeting Friday 17th February @ 15:00 GMT diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17.md new file mode 100644 index 0000000000000000000000000000000000000000..487a25b53d18041a80b50b185198ba364c2bcb31 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-02-17.md @@ -0,0 +1,13 @@ +# Meeting Minutes: Device Identifier WG +## Date: 17th February 2023 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- None outstanding +## Issues +- **[Issue #4](https://github.com/camaraproject/DeviceIdentifier/issues/4) Update commonalities glossary with subproject relevant terms** + - Glossary terms submitted. Issue now closed. +## Discussions +- None +## AOB +- Next meeting Friday 3rd March @ 15:00 GMT diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17.md new file mode 100644 index 0000000000000000000000000000000000000000..2b1942c35e1348ac0730aa2b6c8ec9c34f0f8903 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-17.md @@ -0,0 +1,19 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 17th March 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Chris Howell / Vonage +- Shahram Mohajeri / AT&T +- Jussi Makela / CodeB +- Stefan Engelbert / CodeB +## Pull Requests +- None outstanding +## Issues +- None outstanding +## Discussions +- **API Overview** + - Eric gave a brief overview of the API for new attendees +## AOB +- Next meeting Friday 31st March @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31.md new file mode 100644 index 0000000000000000000000000000000000000000..98ac5b8878100647c683c4b0ae4addd0bc27dcd9 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-03-31.md @@ -0,0 +1,17 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 31st March 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- **[PR #13](https://github.com/camaraproject/DeviceIdentifier/pull/13) Update CAMARA Device Identifier API.yaml** + - Specification changes to be compliant with current design and documentation guidelines in Commonalities WG + - Will be merged by CoB 6th April if no comments +## Issues +- None Outstanding +## Discussions +- **Meeting Cadence** + - Agreed to make meetings monthly given low meeting attendance and dependencies on other CAMARA working groups and sub-projects +## AOB +- Next meeting Friday 28th April @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28.md new file mode 100644 index 0000000000000000000000000000000000000000..222cb42347c0bf8f6e8b64e757a0b98a65e74486 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-04-28.md @@ -0,0 +1,26 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 28th April 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Chris Howell / Vonage +- Shahram Mohajeri / AT&T +- Jussi Makela / CodeB +- Nevin Aquinas / Vodafone +## Pull Requests +- None open +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Proposal is to return an additional device identifer if the primary device is associated with a secondary device (such as a smartwatch). The end user will know that they have such a device, but may not know any idenifiers for the SIM being used in that device. + - Ludovic asked how the mobile network would be aware of this association. Eric to update the issue with more information. +- **[Issue #20](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Documentation needs to be updated given decision in Commonalities to embed documentation in API OAS definition using markdown and HTML + - Eric to open PR with proposed documentation before next meeting +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Some property names used in the API definition do not match those in the Commonalities glossary. Additionally, some terms used in the API are not in the glossary. + - Eric to update names along with adding documentation, and also to submit PR to update glossary as appropriate. +## Discussions +- None +## AOB +- Next meeting Friday 26th May @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26.md new file mode 100644 index 0000000000000000000000000000000000000000..2aa1c2279a5fb8f03b4aa49ac4d7059b28e6f74b --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-05-26.md @@ -0,0 +1,20 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 26th May 2023 +## Attendees +- Eric Murray / Vodafone +- Toshiyasu Wakayama / KDDI +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Adds documentation to API description + - Will be approved and merged before next meeting if no comments before +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Additional information provided on how secondary devices associated with the primary MSISDN are identified +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - No update +- **[Issue #16](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Will be closed by [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) +## Discussions +- None open +## AOB +- Next meeting Friday 23rd June @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23.md new file mode 100644 index 0000000000000000000000000000000000000000..4e2894dc444389174bd96ff43840c82bb751984d --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-06-23.md @@ -0,0 +1,26 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 23rd June 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +- Tim Kittel / Rohde & Schwarz +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Adds documentation to API description + - Request to add indication of supporting network element as SCEF / NEF does not provide IMEI + - In this case, IMEI can be obtained from PCRF over Rx interface. Suggested implementation to be added to documentation. + - Will be approved and merged before next meeting if no other comments before + - Following update will be to replace GET with POST as this method is now approved in CAMARA Design Guidelines +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Additional information provided on how secondary devices associated with the primary MSISDN are identified + - Issue discussed, but no update +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - No update, waiting for approval of [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24). +- **[Issue #16](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Will be closed by [PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) +## Discussions +- None open +## AOB +- Next meeting Friday 21st July @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21.md new file mode 100644 index 0000000000000000000000000000000000000000..face3620e97fa240af70373a6fda1c4923508e5c --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-07-21.md @@ -0,0 +1,25 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 21st July 2023 +## Attendees +- Eric Murray / Vodafone +- Ludovic Robert / Orange +- Rafal Artych / Deutsche Telekom +## Pull Requests +- **[PR #24](https://github.com/camaraproject/DeviceIdentifier/pull/24) Add API documentation to OAS definition v0.3.0** + - Approved and merged +- **[PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27) Update CAMARA Device Identifier API.yaml** + - Changes method of sensitive input parameters from GET headers to POST body following update to CAMARA API design guidelines + - This change would bring Device Identifier API into line with other APIs that use this method of passing sensitive parameters (e.g. Device Status, Device Location) + - PR to remain open for now in case of any discussion. Can be approved at next meeting if no objections. +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - No update, but no appetite to progress this + - Will be closed at next meeting if no other CAMARA participants express a requirement for this functionality +- **[Issue #20](https://github.com/camaraproject/DeviceIdentifier/issues/20) Documentation** + - Now closed +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Waiting for approval of [PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27). +## Discussions +- None open +## AOB +- Skipping August meeting due to holidays, so next meeting will be Friday 15th September @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15.md b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15.md new file mode 100644 index 0000000000000000000000000000000000000000..060072c4531af50c9eaa8224aefaaf4d3d17a5b3 --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/MoM-DVI-2023-09-15.md @@ -0,0 +1,24 @@ +# Meeting Minutes: Device Identifier Sub-Project +## Date: 15th September 2023 +## Attendees +- Eric Murray / Vodafone +## Pull Requests +- **[PR #27](https://github.com/camaraproject/DeviceIdentifier/pull/27) Update CAMARA Device Identifier API.yaml** + - Changes method of sensitive input parameters from GET headers to POST body following update to CAMARA API design guidelines + - This change would bring Device Identifier API into line with other APIs that use this method of passing sensitive parameters (e.g. Device Status, Device Location) + - **PR approved as no comments. Can be now merged.** +- **[PR #29](https://github.com/camaraproject/DeviceIdentifier/pull/29) Update README.md** + - Add links to Swagger Editor and ReDoc formatted versions of current WIP specification + - **PR approved as no comments. Can now be merged.** +## Issues +- **[Issue #19](https://github.com/camaraproject/DeviceIdentifier/issues/19) Secondary Devices** + - Issue to be closed as no interest +- **[Issue #21](https://github.com/camaraproject/DeviceIdentifier/issues/21) API Definition Terminology** + - Can be progressed with conclusion to be agreed at next meeting +- **[Issue #30](https://github.com/camaraproject/DeviceIdentifier/issues/30) Security Schemes and Scopes for Device Identifier API** + - New issue containing proposal for security schemes and scopes to be adopted by the Device Identifier API + - Will leave open for comments until next meeting +## Discussions +- None open +## AOB +- Next meeting will be Friday 13th October @ 15:00 BST diff --git a/original/DeviceIdentifier/documentation/MeetingMinutes/README.md b/original/DeviceIdentifier/documentation/MeetingMinutes/README.md new file mode 100644 index 0000000000000000000000000000000000000000..2a3972374fbd349882c465795f114ce4934b0c2a --- /dev/null +++ b/original/DeviceIdentifier/documentation/MeetingMinutes/README.md @@ -0,0 +1 @@ +Later meeting minutes can now be found in the CAMARA wiki [here](https://wiki.camaraproject.org/display/CAM/Device+Identifier+Meeting+Minutes) diff --git a/original/DeviceIdentifier/documentation/SupportingDocuments/README.MD b/original/DeviceIdentifier/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..38efecab2903648866bb8d5f867fab0e77ea71c6 --- /dev/null +++ b/original/DeviceIdentifier/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/original/DeviceLocation/README.md b/original/DeviceLocation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8ad030fd09c725a5458b81416e76e6705a66c8b2 --- /dev/null +++ b/original/DeviceLocation/README.md @@ -0,0 +1,63 @@ + + + + + + + + + +# DeviceLocation + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceLocation Service API(s) within the Sub Project [Device Location](https://lf-camaraproject.atlassian.net/wiki/x/wgApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/GDLe) + +## Scope +* Service APIs for “Device Location” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * verify the location of a device (location-verification). + * retrieve the location of a device (location-retrieval). + * subscribe and receive notifications about a device entering or leaving certain location (geofencing-subscriptions). + * NOTE: The scope of these APIs is limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/DeviceLocation/releases/tag/r3.2) (Fall25), with the following API versions: + * **geofencing-subscriptions v0.5.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/geofencing-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/geofencing-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/geofencing-subscriptions.yaml) + * **location-retrieval v0.5.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/location-retrieval.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-retrieval.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-retrieval.yaml) + * **location-verification v3.0.0** + [[YAML]](https://github.com/camaraproject/DeviceLocation/blob/r3.2/code/API_definitions/location-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceLocation/r3.2/code/API_definitions/location-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceLocation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceLocation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceLocation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + - Schedule: bi-weekly (odd weeks), Tuesday, 8:00 AM UTC (9:00 CET/10:00 CEST) + - Meeting link: [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91878854906?password=7e620a89-fcb5-4d2d-927a-17e3a0d1d28e) +* Mailing list: + - To subscribe / unsubscribe to the mailing list of this Sub Project, please visit . + - A message to the community of this Sub Project can be sent using . +* Slack channel: [camara-project.slack.com](https://join.slack.com/t/camara-project/shared_invite/zt-26gy3e64n-o7Riy3MoXmzdaDEL3wlngg) #sp-device-location diff --git a/original/DeviceLocation/code/API_definitions/geofencing-subscriptions.yaml b/original/DeviceLocation/code/API_definitions/geofencing-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..7e79a1503e2af76d6cb00457f5372c5728836730 --- /dev/null +++ b/original/DeviceLocation/code/API_definitions/geofencing-subscriptions.yaml @@ -0,0 +1,1787 @@ +openapi: 3.0.3 +info: + title: Device Geofencing Subscriptions + description: | + API to create, retrieve and delete event subscriptions to realize geofencing for a user device. + + # Introduction + + With this API, API consumers can create subscriptions for their devices to receive notifications when a device enters or exits a specified area. + + * If the provided area is out of the operator's coverage or it is not supported for any reason, an error `422 GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED` will be returned. + * Legal restrictions regarding privacy, or other regulatory or implementation issues, may force the operator to set restrictions to the provided area, such as setting a minimum value to the accepted radius. In these cases, an error `422 GEOFENCING_SUBSCRIPTIONS.INVALID_AREA` will be returned and the error message will refer to the reason of the limitation. + + The area provided in the request is described by a circle determined by coordinates (latitude and longitude) and an accuracy defined by the radius. + + Upon successfully creating a subscription, the API will provide an Event Subscription ID, and it will indicate the subscription's expiration date. + + If the geofencing-state of a device changes, the event subscriber will be notified back to the provided Notification-Url given by the subscription-request. + + Device geofencing API could be useful in scenarios such as: + + - Tracking devices for Presetting of Home-Settings + - Tracking of logistics + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface which a device is planned to enter or exit. + + # API Functionality + + The API exposes following capabilities: + + ## Device Geofencing subscription + These endpoints allow to manage event subscription on geofencing device location event. + + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.geofencing-subscriptions.v0.area-entered`` - Event triggered when the device enters the given area + + - ``org.camaraproject.geofencing-subscriptions.v0.area-left`` - Event triggered when the device leaves the given area + + Note: Additionally, the following events could be send, which do not require a dedicated subscription: + - `org.camaraproject.geofencing-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.geofencing-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.geofencing-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used when: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + - the specified geofence-`area` cannot be covered or is too small to be managed + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding geofencing can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may behave: + + - rejecting the subscription with an error indicating that that phone number is not supported for this API, or + - generating events for a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - generating events for of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/DeviceLocation + +servers: + - url: "{apiRoot}/geofencing-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Geofencing subscriptions + description: Operations to manage event subscriptions on geofencing events for leaving and entering an area. +paths: + /subscriptions: + post: + tags: + - Geofencing subscriptions + summary: "Create a geofencing subscription for a device" + description: Create a subscription for a device to receive notifications when the device enters or exits a specified area. + operationId: createGeofencingSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - geofencing-subscriptions:org.camaraproject.geofencing-subscriptions.v0.area-entered:create + - geofencing-subscriptions:org.camaraproject.geofencing-subscriptions.v0.area-left:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + CIRCLE_AREA_ENTERED: + $ref: "#/components/examples/REQUEST_CIRCLE_AREA_ENTERED" + REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS: + $ref: "#/components/examples/REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: This endpoint is to be implemented by the API consumer. + The Geofencing server will call this endpoint whenever a Geofencing event occurs. + The `operationId` value will have to be replaced accordingly with WG API specific semantics. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + CIRCLE_AREA_ENTERED: + $ref: "#/components/examples/CIRCLE_AREA_ENTERED" + CIRCLE_AREA_LEFT: + $ref: "#/components/examples/CIRCLE_AREA_LEFT" + SUBSCRIPTION_STARTED: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + SUBSCRIPTION_UPDATED: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + SUBSCRIPTION_ENDED: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + SUBSCRIPTION_UNPROCESSABLE: + $ref: "#/components/examples/SUBSCRIPTION_UNPROCESSABLE" + responses: + "204": + description: Successful notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - notificationsBearerAuth: [] + - {} + responses: + "201": + description: Created (Successful creation of subscription). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Geofencing subscriptions + summary: "Retrieve a list of geofencing event subscription" + description: Retrieve a list of geofencing event subscription(s). + operationId: retrieveGeofencingSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - geofencing-subscriptions:read + responses: + "200": + description: List of event subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Geofencing subscriptions + summary: "Operation to retrieve a subscription based on the provided ID" + description: Retrieve Geofencing subscription information for a given subscription ID. + operationId: retrieveGeofencingSubscription + security: + - openId: + - geofencing-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Geofencing subscriptions + summary: "Delete a Geofencing event subscription" + operationId: deleteGeofencingSubscription + description: Delete a given Geofencing subscription. + security: + - openId: + - geofencing-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Geofencing subscription deleted. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + description: OpenID Connect authentication. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation. + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ErrorInfo: + description: The error info object for possible error cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code. + code: + type: string + description: A human-readable code to describe the error. + message: + type: string + description: A human-readable description of what the event represents. + + SubscriptionRequest: + description: The request for creating an event-type event subscription. + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types which are eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/ConfigRequest" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now. + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + type: object + properties: + subscriptionExpireTime: + type: string + format: date-time + example: "2023-01-17T13:18:23.682Z" + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + Note on combined usage of `initialEvent` and `subscriptionMaxEvents`: + If an event is triggered following `initialEvent` set to `true`, this event will be counted towards `subscriptionMaxEvents`. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered. + + ConfigRequest: + allOf: + - $ref: "#/components/schemas/Config" + - description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + Specific event type attributes requested by the client must be defined in `subscriptionDetail`. + Note: If a request is performed for several event types, all subscribed events will use the same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetailRequest" + + ConfigResponse: + allOf: + - $ref: "#/components/schemas/Config" + - description: | + Implementation-specific configuration parameters are needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent`. + Specific event type attributes granted by the implementation are included in `subscriptionDetail`. + Note: If a request is performed for several event types, all subscribed events will use the same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetailResponse" + + + SinkCredential: + type: object + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + properties: + credentialType: + type: string + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetailRequest: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + required: + - area + + SubscriptionDetailResponse: + description: The detail of the event subscription granted by the implementation. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + required: + - area + + SubscriptionEventType: + type: string + description: | + area-entered - Event triggered when the device enters the given area + + area-left - Event triggered when the device leaves the given area + enum: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + - org.camaraproject.geofencing-subscriptions.v0.area-left + + NotificationEventType: + type: string + description: | + area-entered - Event triggered when the device enters the given area + + area-left - Event triggered when the device leaves the given area + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends + enum: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + - org.camaraproject.geofencing-subscriptions.v0.area-left + - org.camaraproject.geofencing-subscriptions.v0.subscription-started + - org.camaraproject.geofencing-subscriptions.v0.subscription-updated + - org.camaraproject.geofencing-subscriptions.v0.subscription-ended + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: As of now we enforce to have only event type per subscription. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/ConfigResponse" + id: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: "1119920371" + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: Response for an event-type subscription request managed asynchronously (Creation or Deletion). + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the API provider might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different API providers. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response or event. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks, it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask. + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number. + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Area: + type: object + description: The geofencing area where the monitor is active. This area is specified by API consumers in the subscription request. The same area definition is included in event notifications without any modifications. + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + enum: + - CIRCLE + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: | + Expected accuracy for the subscription event of device location, in meters from `center`. + Note: The area surface could be restricted locally depending on regulations. Implementations may enforce a larger minimum radius (e.g. 1000 meters). + minimum: 1 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map. + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location. + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component of location. + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + CloudEvent: + description: The notification callback. + required: + - id + - source + - specversion + - type + - time + - data + properties: + id: + type: string + description: Identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/NotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version). + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type. + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.geofencing-subscriptions.v0.area-left: "#/components/schemas/EventAreaLeft" + org.camaraproject.geofencing-subscriptions.v0.area-entered: "#/components/schemas/EventAreaEntered" + org.camaraproject.geofencing-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.geofencing-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.geofencing-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventAreaLeft: + description: Event structure for event when the device leaves the area. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaLeft" + + EventAreaEntered: + description: Event structure for event when the device enters the area. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaEntered" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + - area + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - area + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: Event structure for event subscription ends. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + AreaLeft: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.area-left event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + AreaEntered: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.area-entered event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: | + Event detail structure for org.camaraproject.geofencing-subscriptions.v0.subscription-ended event. + Note that the device object is defined as optional and will only to be returned if provided in createGeofencingSubscription. + If more than one type of device identifier was provided, only one identifier will be returned + (at implementation choice and with the original value provided in createGeofencingSubscription). + type: object + required: + - area + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + area: + $ref: "#/components/schemas/Area" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_UNPROCESSABLE - Subscription cannot be processed due to some reason, e.g. because the specified area cannot be managed. Useful for asynchronous subscription creation. + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_UNPROCESSABLE + - SUBSCRIPTION_EXPIRED + - SUBSCRIPTION_DELETED + - ACCESS_TOKEN_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_PROTOCOL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_PROTOCOL: + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported. + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported. + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Schema validation failed + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + summary: The subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_TOKEN_MISMATCH: + value: + status: 403 + code: SUBSCRIPTION_MISMATCH + message: Inconsistent access token for requested events subscription. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: + Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - SERVICE_NOT_APPLICABLE + - UNNECESSARY_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED + - GEOFENCING_SUBSCRIPTIONS.INVALID_AREA + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GEOFENCING_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: GEOFENCING_SUBSCRIPTIONS.AREA_NOT_COVERED + message: "Unable to cover the requested area" + GEOFENCING_422_INVALID_AREA: + summary: Invalid area + description: The requested area is too small to be supported by the system. + value: + status: 422 + code: GEOFENCING_SUBSCRIPTIONS.INVALID_AREA + message: "The requested area is too small" + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + REQUEST_CIRCLE_AREA_ENTERED: + description: A sample geofence for entering for a circle area. + value: + protocol: "HTTP" + sink: https://notificationSendServer12.supertelco.com + types: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + config: + subscriptionDetail: + device: + phoneNumber: "+12345678912" + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + REQUEST_CIRCLE_AREA_ENTERED_MULTIPLE_IDENTIFIERS: + description: A sample geofence for entering for a circle area. + value: + protocol: "HTTP" + sink: https://notificationSendServer12.supertelco.com + types: + - org.camaraproject.geofencing-subscriptions.v0.area-entered + config: + subscriptionDetail: + device: + phoneNumber: "+12345678912" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + CIRCLE_AREA_ENTERED: + description: The cloud event when a geofence area was entered. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.area-entered + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + CIRCLE_AREA_LEFT: + description: The cloud event when a geofence area was left. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.area-left + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + + SUBSCRIPTION_STARTED: + description: The cloud event when a geofence subscription was started. + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: dv10-h556-rt89-1403 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a geofence subscription was updated. + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: dv10-h556-rt89-1403 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a geofence subscription ended. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + subscriptionId: 987654321 + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + terminationReason: SUBSCRIPTION_EXPIRED + + SUBSCRIPTION_UNPROCESSABLE: + description: The cloud event when the subscription process was aborted. + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.geofencing-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2023-03-22T05:40:23.682Z + data: + device: + phoneNumber: +123456789 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + terminationReason: SUBSCRIPTION_UNPROCESSABLE + terminationDescription: The requested area cannot be covered by the network. diff --git a/original/DeviceLocation/code/API_definitions/location-retrieval.yaml b/original/DeviceLocation/code/API_definitions/location-retrieval.yaml new file mode 100644 index 0000000000000000000000000000000000000000..31f19e5499c7a4eaa5c5c503d6b837cdf2af0bd1 --- /dev/null +++ b/original/DeviceLocation/code/API_definitions/location-retrieval.yaml @@ -0,0 +1,683 @@ +openapi: 3.0.3 +info: + title: Device Location Retrieval + description: | + This API provides the ability to retrieve a device location. + + # Introduction + + With this API, API consumers can retrieve the area where a certain user device is localized. + The area provided in the response could be described: + - by a circle determined by coordinates (latitude and longitude) and a radius. + - by a simple polygon delimited by segments connecting consecutively an array of coordinates (points). The last point connects to the first point to delimit a closed shape bounded with straight sides. + + The retrieved shape depends on the network conditions at the device's location and any of the supported shapes could be received. + + The requester could optionally ask for + * a freshness of the localization information by providing a `maxAge` ("I want a location not older than 600 seconds"). + * an accuracy of the localization information by providing a `maxSurface` ("I want a location not larger than 1000000 square meters"). + + + The result accuracy depends on the network's ability and accuracy to locate the device. + + Additionally to location information, the answer will also provide indication about the location time. + + Location retrieval API could be useful in scenarios such as: + + - Fraud protection to ensure a given user is located in the region, country or location authorized for financial transactions + - Verify the GPS coordinates reported by the app on a device to ensure the GPS was not faked e.g. for content delivery with regional restrictions + - Contextual-based advertising, to trigger advertising after verifying the device is in the area of interest + + - Smart Mobility (Vehicle/bikes renting): obtain the location of a vehicle/bike to guarantee they are rented correctly + + **Note**: Location is in most jurisdictions considered to be sensitive data and thereby consent by device owner/user must be verified before providing it to the developer. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface where a device may be physically located. + + * **Max Age**: Maximum age of the location information which is accepted for the location retrieval (in seconds). + + * Absence of `maxAge` means that "any age" is acceptable for the client. In other words, this is like `maxAge`=infinite. The system will return `lastLocationTime` in the response. If the system is not able to provide location, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_LOCATE is sent back. + * `maxAge`=0 means that a fresh calculation is requested by the client. If the system is not able to provide the fresh location, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE is sent back. + + * **Last Location Time** : Last date and time when the device was localized. + + * **Max Surface**: Maximum surface in square meters which is accepted by the client for the location retrieval. + + * absence of `maxSurface` means that "any surface size" is acceptable for the client. + * API implementation could specify the minimum acceptable `maxSurface` in the documentation (for example a minimum of 10000 square meters are allowed). + * If the system is not able to provide an area with a surface acceptable with the client request, an error 422 with code LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE is sent back. + * Note: if both `maxAge` and `maxSurface` requirements fail, the system can either send back one or the other error code. + + # API Functionality + + The API exposes a single endpoint/operation: + + - `/retrieve` : Retrieve where the device is localized. + The operation returns: + * a localization defined either as a circle, with the center specified by the latitude and longitude, and a radius for answer accuracy, or as polygon defined by the array of points delimiting its boundary. + * a timestamp with the location information freshness. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may response with: + + - an error indicating that that phone number is not supported for this API, or + - the location of a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - a location value that combines the location of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/DeviceLocation +servers: + - url: '{apiRoot}/location-retrieval/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Location retrieval + description: Retrieve the location of a device +paths: + /retrieve: + post: + tags: + - Location retrieval + summary: 'Execute location retrieval for a user device' + description: Retrieve the area where a certain user device is localized. + operationId: retrieveLocation + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/RetrievalLocationRequest' + examples: + INPUT_PHONE_NUMBER_MAX_AGE: + summary: Phone number and maxAge + description: Retrieve location for a device identified by a phone number, providing a maxAge + value: + device: + phoneNumber: "+123456789" + maxAge: 120 + INPUT_PHONE_NUMBER_MAX_AGE_AND_SURFACE: + summary: Phone number, maxAge and maxSurface + description: Retrieve location for a device identified by a phone number, providing a maxAge and maxSurface + value: + device: + phoneNumber: "+123456789" + maxAge: 120 + maxSurface: 1000000 + INPUT_IP_ADDRESS_V4: + summary: IPv4 address without maxAge + description: Retrieve location for a device identified by an IPv4 address, without an indication for maxAge + value: + device: + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + INPUT_NO_DEVICE_AND_MAX_AGE: + summary: Device not provided, only maxAge + description: The device has to be deducted from token + value: + maxAge: 120 + INPUT_PHONE_NUMBER_IP_ADDRESS_V4: + summary: Both phone number and IPv4 address, without maxAge + description: Retrieve location for a device identified both by a phone number and an IPv4 address, without an indication for maxAge + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + responses: + '200': + description: Location retrieval result + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/Location' + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + LOCATION_CIRCLE_WITH_DEVICE: + $ref: "#/components/examples/LOCATION_CIRCLE_WITH_DEVICE" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/RetrieveLocationNotFound404' + '422': + $ref: '#/components/responses/RetrieveLocationUnprocessableEntity422' + security: + - openId: + - location-retrieval:read + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RetrievalLocationRequest: + description: Request to retrieve the location of a device. Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: '#/components/schemas/Device' + maxAge: + type: integer + minimum: 0 + description: Maximum age of the location information which is accepted for the location retrieval (in seconds). Absence of maxAge means "any age" and maxAge=0 means a fresh calculation. + maxSurface: + type: integer + minimum: 1 + description: Maximum surface in square meters which is accepted by the client for the location retrieval. Absence of maxSurface means "any surface size". + example: 1000000 + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Location: + type: object + description: Device location + required: + - lastLocationTime + - area + properties: + lastLocationTime: + $ref: "#/components/schemas/LastLocationTime" + area: + $ref: '#/components/schemas/Area' + device: + $ref: "#/components/schemas/DeviceResponse" + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + LastLocationTime: + description: Last date and time when the device was localized. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + format: date-time + type: string + example: "2023-09-07T10:40:52Z" + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + RetrieveLocationNotFound404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + summary: Identifier not found + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + RetrieveLocationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE + - LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE + - LOCATION_RETRIEVAL.UNABLE_TO_LOCATE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + summary: Missing identifier + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + summary: Unsupported identifier + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + summary: Unnecessary identifier + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + LOCATION_RETRIEVAL_422_UNABLE_TO_FULFILL_MAX_AGE: + summary: Unable to fulfill maxAge + description: The system is not able to provide the fresh location required by the client + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_AGE + message: "Unable to provide expected freshness for location" + LOCATION_RETRIEVAL_422_UNABLE_TO_FULFILL_MAX_SURFACE: + summary: Unable to fulfill maxSurface + description: The system is not able to provide accurate acceptable surface required by the client + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_FULFILL_MAX_SURFACE + message: "Unable to provide accurate acceptable surface for location" + LOCATION_RETRIEVAL_422_UNABLE_TO_LOCATE: + summary: Unable to locate device + description: The network cannot locate the device + value: + status: 422 + code: LOCATION_RETRIEVAL.UNABLE_TO_LOCATE + message: "The network is unable to locate the device" + examples: + RETRIEVAL_CIRCLE: + summary: circle-based device location retrieval + description: The device is localized within a circle with a center at the specified coordinates and a radius of 800 meters. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + RETRIEVAL_POLYGON: + summary: polygon-based device location retrieval + description: The device is localized within a polygon delimited by the provided coordinates. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.752490 + longitude: 4.861876 + - latitude: 45.751224 + longitude: 4.861125 + - latitude: 45.751442 + longitude: 4.859827 + LOCATION_CIRCLE_WITH_DEVICE: + summary: circle-based device location retrieval, returning the device identifier used by the implementation + description: The device is localized within a circle with a center at the specified coordinates and a radius of 800 meters. Response when the request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier. + value: + lastLocationTime: "2023-10-17T13:18:23.682Z" + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + device: + phoneNumber: "+123456789" diff --git a/original/DeviceLocation/code/API_definitions/location-verification.yaml b/original/DeviceLocation/code/API_definitions/location-verification.yaml new file mode 100644 index 0000000000000000000000000000000000000000..375d2674cb5268f960c83483bea49f55d3043e20 --- /dev/null +++ b/original/DeviceLocation/code/API_definitions/location-verification.yaml @@ -0,0 +1,688 @@ +openapi: 3.0.3 +info: + title: Device Location Verification + description: | + This API provides the consumer with the ability to verify the location of a device. + + # Introduction + + API consumers are able to verify whether the location of certain user device is within the area specified. Currently the only area supported as input is a circle determined by a set of coordinates (latitude and longitude) and some expected accuracy (radius). + + * If the provided area is out of the operator's coverage or it is not supported for any reason, an error `422 LOCATION_VERIFICATION.AREA_NOT_COVERED` will be returned. + * Legal restrictions regarding privacy, or other regulatory or implementation issues, may force the operator to set restrictions to the provided area, such as setting a minimum value to the accepted radius. In these cases, an error `422 LOCATION_VERIFICATION.INVALID_AREA` will be returned and the error message will refer to the reason of the limitation. + + The verification result depends on the network's ability and accuracy to locate the device at the requested area. + + * If the network's estimation of the device's location is fully contained within the requested area, the verification result is `TRUE`. + * If the network's estimation of the device's location does not overlap with the requested area at all, the verification result is `FALSE`. + * If the network's estimation of the device's location partially overlaps with the requested area, or it fully contains the requested area (because it is larger), the result is `PARTIAL`. In this case, a `match_rate` is included in the response, indicating an estimation of the likelihood of the match in percent. + * If the network cannot locate the device, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_LOCATE` is sent back. + * The client may optionally include a `maxAge` indication. If the location information known to the server is older than the specified `maxAge` or not known at all, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE` is sent back, independently of the verification result. + + Location Verification could be useful in scenarios such as: + + - Fraud protection, to ensure a given user is located in the location area claimed for financial transactions. + - Verification of GPS coordinates reported by the app on a device, to ensure the GPS was not faked, e.g. for content delivery with regional restrictions. + - Contextual-based advertising, to trigger advertising after verifying the device is in the area of interest. + - Smart mobility (vehicle / bikes renting), to confirm the location of the device and the location of the vehicle/bike to guarantee they are rented correctly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + * **Area**: It specifies the geographical surface where a device may be physically located. + + * **Max Age**: Maximum age of the location information which is accepted for the location verification (in seconds). + * Absence of maxAge means "any age" is acceptable for the client. In other words, this is like maxAge=infinite. In this case the system will return `lastLocationTime`. + * maxAge=0 means a fresh calculation is requested by the client. If the system is not able to provide the fresh location, an error with code `422 LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE` is sent back. + + + * **Verification**: Process triggered in the API server to confirm or contradict the expectation assumed by the API client about the device location. + + # API Functionality + + The API exposes a single endpoint/operation: + + - Verify whether the device location is within a requested area, currently a circle with center specified by the latitude and longitude, and radius specified by the accuracy. The operation returns a verification result and, optionally, a match rate estimation for the location verification in percent. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios, where more than one mobile device is associated with the phone number given as input in the API call (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device whose location is to be verified. Check with the API provider what is the expected behaviour when a phone number belonging to a multi-SIM group is used as the device identifier, as the API may response with: + + - an error indicating that that phone number is not supported for this API, or + - the verification for a single device in the multi-SIM group, if one of the devices is considered linked to the main SIM and this concept is supported by the operator, or + - a verification value that combines the location verification of all the SIMs associated to the requested phone number. + + Possible solutions to make the scenario more deterministic include: + + - Using preferably the authorisation code flow to obtain an access token, which will automatically identify the intended device. + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port. + - Check with the API provider whether a unique "secondary" phone number is already associated with each device and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: tbd +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/DeviceLocation +servers: + - url: "{apiRoot}/location-verification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Location verification + description: Verification of the location of a device +paths: + /verify: + post: + tags: + - Location verification + summary: Verify the location of a device + description: | + Verify whether the location of a device is within a requested area. The operation returns a verification result and, optionally, a match rate estimation for the location verification in percent. + operationId: verifyLocation + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/VerifyLocationRequest" + examples: + INPUT_PHONE_NUMBER_CIRCLE: + summary: Phone number, circle and maxAge + description: Verify if device identified by a phone number is within a circle, providing a maxAge + value: + device: + phoneNumber: "+123456789" + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + INPUT_IP_ADDRESS_V4_CIRCLE: + summary: IPv4 address, circle, without maxAge + description: Verify if device identified by an IPv4 address is within a circle, not indicating a maxAge + value: + device: + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + INPUT_PHONE_NUMBER_IP_ADDRESS_V4_CIRCLE: + summary: Both phone number and IPv4 address, circle and maxAge + description: Verify if device identified both by a phone number and an IPv4 address is within a circle, providing a maxAge + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: 123.234.1.2 + publicPort: 1234 + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + INPUT_NO_DEVICE: + summary: Device not provided + description: The device has to be deducted from token + value: + area: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + maxAge: 120 + responses: + "200": + description: Location verification result + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/VerifyLocationResponse" + examples: + VERIFICATION_TRUE: + summary: Match + description: The network locates the device within the requested area + value: + verificationResult: "TRUE" + lastLocationTime: "2023-09-07T10:40:52Z" + VERIFICATION_TRUE_WITH_DEVICE: + summary: Match returning the device identifier used by the implementation + description: The network locates the device within the requested area. Response when the request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + verificationResult: "TRUE" + lastLocationTime: "2023-09-07T10:40:52Z" + device: + phoneNumber: "+123456789" + VERIFICATION_FALSE: + summary: No match + description: The requested area does not match the area where the network locates the device + value: + verificationResult: "FALSE" + lastLocationTime: "2023-09-07T10:40:52Z" + VERIFICATION_PARTIAL: + summary: Partial match + description: The requested area partially matches the area where the network locates the device + value: + verificationResult: "PARTIAL" + matchRate: 74 + lastLocationTime: "2023-09-07T10:40:52Z" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/VerifyLocationNotFound404" + "422": + $ref: "#/components/responses/VerifyLocationUnprocessableEntity422" + security: + - openId: + - location-verification:verify +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + enum: + - CIRCLE + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: | + Expected accuracy for the verification, in meters from `center`. + Note: The area surface could be restricted locally depending on regulations. Implementations may enforce a larger minimum radius (e.g. 1000 meters). + minimum: 1 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + VerifyLocationRequest: + description: Request to verify the location of a device. Device is not required when using a 3-legged access token, following the rules in the description. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + area: + $ref: "#/components/schemas/Area" + maxAge: + $ref: "#/components/schemas/MaxAge" + required: + - area + + VerifyLocationResponse: + description: Response to a location verification request + type: object + required: + - verificationResult + - lastLocationTime + properties: + verificationResult: + $ref: "#/components/schemas/VerificationResult" + lastLocationTime: + $ref: "#/components/schemas/LastLocationTime" + matchRate: + $ref: "#/components/schemas/MatchRate" + device: + $ref: "#/components/schemas/DeviceResponse" + + Device: + description: | + End-user device able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the API provider might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different API providers. In this case the identifiers MUST belong to the same device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the response. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + MaxAge: + description: The maximum age (in seconds) for the location known by the implementation, which is accepted for the verification. Absence of maxAge means "any age" and maxAge=0 means a fresh calculation. + type: integer + minimum: 0 + example: 120 + + VerificationResult: + description: | + Result of a verification request: + - `TRUE`: when the network locates the device within the requested area, + - `FALSE`: when the requested area does not match the area where the network locates the device, + - `PARTIAL`: when the requested area partially match the area where the network locates the device. A `match_rate` is included in the response. + type: string + enum: + - "TRUE" + - "FALSE" + - "PARTIAL" + + MatchRate: + description: Estimation of the match rate between the area in the request (R), and area where the network locates the device (N), calculated as the percent value of the intersection of both areas divided by the network area, that is (R ∩ N) / N * 100. Included only if VerificationResult is PARTIAL. + type: integer + minimum: 1 + maximum: 99 + + LastLocationTime: + description: Timestamp of the last location information. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-09-07T10:40:52Z" + format: date-time + type: string + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + VerifyLocationNotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + VerifyLocationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - LOCATION_VERIFICATION.AREA_NOT_COVERED + - LOCATION_VERIFICATION.INVALID_AREA + - LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE + - LOCATION_VERIFICATION.UNABLE_TO_LOCATE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + LOCATION_VERIFICATION_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: LOCATION_VERIFICATION.AREA_NOT_COVERED + message: "Unable to cover the requested area" + LOCATION_VERIFICATION_422_INVALID_AREA: + summary: Invalid area + description: The requested area is too small to be supported by the system. + value: + status: 422 + code: LOCATION_VERIFICATION.INVALID_AREA + message: "The requested area is too small" + LOCATION_VERIFICATION_422_UNABLE_TO_FULFILL_MAX_AGE: + summary: Unable to fulfill maxAge + description: The system is not able to provide the fresh location required by the client + value: + status: 422 + code: LOCATION_VERIFICATION.UNABLE_TO_FULFILL_MAX_AGE + message: "Unable to provide expected freshness for location" + LOCATION_VERIFICATION_422_UNABLE_TO_LOCATE: + summary: Unable to locate device + description: The network cannot locate the device + value: + status: 422 + code: LOCATION_VERIFICATION.UNABLE_TO_LOCATE + message: "The network is unable to locate the device" diff --git a/original/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist.md b/original/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..c6bbe33dfc3aa548332f025f8a189e42f65ca5db --- /dev/null +++ b/original/DeviceLocation/documentation/API_documentation/geofencing-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for geofencing-subscriptions 0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                                                                  initial | public-release
                                                                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/geofencing-subscriptions.yaml](/code/API_definitions/geofencing-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/geofencing-subscriptions.feature](/code/Test_definitions/geofencing-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/geofencing-subscriptions.feature](/code/Test_definitions/geofencing-subscriptions.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/ugHWB) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist.md b/original/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..c0f26d1c2562c8d3b65b7904e04486411f5f941f --- /dev/null +++ b/original/DeviceLocation/documentation/API_documentation/location-retrieval-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for location-retrieval 0.5.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                                                                  initial | public-release
                                                                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/location-retrieval.yaml](/code/API_definitions/location-retrieval.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/location-retrieval.feature](/code/Test_definitions/location-retrieval.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/location-retrieval.feature](/code/Test_definitions/location-retrieval.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AQBqBQ) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist.md b/original/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..d612b255b0badf199be1ec07e29571de0992872a --- /dev/null +++ b/original/DeviceLocation/documentation/API_documentation/location-verification-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for location-verification 3.0.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                                                                  initial | public-release
                                                                  stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------------------------:|:-------------------------:|:------:|:--------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/location-verification.yaml](/code/API_definitions/location-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/location-verification-User-Story.md](/documentation/API_documentation/location-verification-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/location-verification.feature](/code/Test_definitions/location-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/location-verification.feature](/code/Test_definitions/location-verification.feature) | +| 9 | Test result statement | O | O | O | M | ? | https://github.com/camaraproject/DeviceLocation/issues/371 | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/F4BpBQ) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceLocation/documentation/API_documentation/location-verification-User-Story.md b/original/DeviceLocation/documentation/API_documentation/location-verification-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..960d0295bf6f8f83388a314cfabbf66ea8f2caae --- /dev/null +++ b/original/DeviceLocation/documentation/API_documentation/location-verification-User-Story.md @@ -0,0 +1,11 @@ +# Location Verification API User Story + + +| **Item** | **Details** | +|------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------| +| ***Summary*** | As an enterprise application developer, I want to verify the location of a user's device, so that I can ensure the device is within a specified area for security and contextual-based services. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                                  **Scope:**
                                                                  - Verifies if the specified device is located within a predefined geographical area (e.g.circle with given coordinates and radius, polygon...). | +| ***Pre-conditions*** | The preconditions are listed below:
                                                                  1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform.
                                                                  2. The ASP:BusinessManager has successfully subscribed to the Location Verification API product from the product catalog via (or not) a Channel Partner.
                                                                  3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                                                  4. The ASP:User performs an authorization request to CSP
                                                                  5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                                  6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API. | +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Location Verification API providing the End-User's device identifier (e.g., phone number), the area information (center coordinates and radius, polygon...) and the maximum age of the location information.
                                                                    **Ends when:** The CSP's Location Verification server responds with the verification result indicating if the End-User's device is within the specified area, partially matches the area, or is unknown. When the device partially matches the area, the server additionally responds with a match-rate, which defines a percent value of the intersection of both areas. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the End-User's device location. | +| ***Exceptions*** | Several exceptions might occur during the Location Verification API operations
                                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                    - Incorrect input data (e.g., malformed phone number).
                                                                    - Not able to provide: Network unable to locate the device due to various reasons (e.g., device not connected, outdated location data). | diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31.md new file mode 100644 index 0000000000000000000000000000000000000000..8c00daed707983f60f96151aa81bc70c84cd2415 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-01-31.md @@ -0,0 +1,44 @@ +# CAMARA DeviceLocation meeting - 2023-01-31 + +*January 31st, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Noel Wirzius (DT) +* Patrice Conil (Orange) +* Rafal Artych (DT) +* Robert Ludovic (orange) +* Udaka Kappagoda (Axiata Digital Labs) +* Vaibhav Metha () +* 정윤선님 Serena () + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introductions +* Overview of release management +* Review WoW for new proposals +* Open issues and PRs +* Noel from DT would like to present a couple of points +* TEF to propose enhancement of the response to cover partial matches +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Release management | Current version tagged as v0.1.0.
                                                                    Versioning still being discussed in Commonalities.
                                                                    We have a dev-v0.2.0 branch where new PRs are proposed, but other WGs are pulling PRs directly to main. | Waiting for decision on Commonalities and align with them | +| WoW | - First we should open a new issue to propose anything new. Get feedback and comments on issue.
                                                                    - After some agreement, open a PR with details.
                                                                    - To merge a PR we need at least 2 approvals, including Code Owners. | Reminder on the 'rules of engagement' | +| Add `maxAge` | [PR #9](https://github.com/camaraproject/DeviceLocation/pull/9) proposing new request parameter. Discussion on the PR still open | - Discussion of parameter position - should be in request/response?
                                                                    - Tracking history of a location is not a API issue but related to network capabilities.
                                                                    - UC: logistic to track shipment. Give access to people when they enter a building. Fraud tracking. Launching a app for a limited perimeter
                                                                    - Reminder: this is not a 'precise' response as a minimum 2km radius is considered

                                                                    **@Udaka triggers an issue & check with Geo fencing** | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12).
                                                                    We must adapt errors and properties to guidelines | Waiting for decision on Commonalities and other WGs, and align with them | +| New points by DT | DT is currently working on an implementation against the nef and also I would love to discussss a new feature – subscription based tracking. | DT Improvements proposal:
                                                                    - Subscription based (when a sim card enters a perimeter)
                                                                    - Add a new response value for 'unknown'
                                                                    - Get the cell location for a device

                                                                    **@DT: Create new issue for each of them** | +| Covering partial matches (TEF) | [Issue TBC] Current response with a single boolean leaves some ambiguous scenarios where there are partial matches. | - How to manage partial matches as several 'in middle' scenarios are possible

                                                                    **@José (Telefonica) opens an issue for this.** | + + +## AOB + +* Next call is on February 14th. \ No newline at end of file diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14.md new file mode 100644 index 0000000000000000000000000000000000000000..0d2ddbc066f42f0b9e90678919e27999b62c7d09 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-02-14.md @@ -0,0 +1,35 @@ +# CAMARA DeviceLocation meeting - 2023-02-14 + +*February 14th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* José Luis Urien (Telefónica) +* Noel Wirzius (DT) +* Rafal Artych (DT) +* 若山 敏康 () + + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| YAML Update: add UNKNOWN for verify location | [PR #22](https://github.com/camaraproject/DeviceLocation/pull/22)
                                                                    - Review if ready for merging | Pending on a second approval, **please @bigludo7 review** | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - New error format approved in Commonalities
                                                                    - New model for `UeId` is being discussed in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG | - **@jlurien to create PR to align errors to new error model**

                                                                    - Wait until discussions on new model for `UeId` are completed in QualityOnDemand and align with them | +| Enhancing response to cover partial matches | [Issue #20](https://github.com/camaraproject/DeviceLocation/issues/20)
                                                                    - No feedback, so far. Discuss if ready for PR | - **@all Give feedback to issue** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18)
                                                                    - No feedback, so far. Discuss if ready for PR | - **@all Give feedback to issue** | +| Add `maxAge` | Pending action from last meeting:

                                                                    **@Udaka triggers an issue & check with Geo fencing** | - **@NoelWirzius to open new issue** | + + +## AOB + +* Next call is on February 28th. \ No newline at end of file diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14.md new file mode 100644 index 0000000000000000000000000000000000000000..7c5269798030164b53c73f15e1c0a79a1856a4c1 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-14.md @@ -0,0 +1,64 @@ +# CAMARA DeviceLocation meeting - 2023-03-14 + +*March 14th, 2023* + +## Attendees + +* Agustín Martín (Telefónica) +* Akos Hunyadi (DT) +* Inés Vidal (Telefónica) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Rafal Artych (DT) +* Robert Ludovic (Orange) +* Shuting Qing (Huawei) +* Tuan Tran (Broadpeak) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* WoW: PRs to main branch +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - New error format approved in Commonalities
                                                                    - New model for `UeId` is being discussed in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. New terms agreed, pending to be submitted to Commonalities | - ~~**@jlurien to create PR to align errors to new error model**~~ [Merged](https://github.com/camaraproject/DeviceLocation/pull/28)

                                                                    - Wait until discussions on new model for `UeId` are completed in QualityOnDemand and align with them.

                                                                    - **Team OK with the change**| +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                                                                    - Some feedback by Orange and Telefónica
                                                                    - Some pending comments: Add DELETE and GET, support for susbcription termination due to consent removal (new event?) | - Valid enhancement from the team
                                                                    - Need alignment & feedback with other API (topic raised in Commonalities)

                                                                    - **Keep it open for further discussion** | +| Enhancing response to cover partial matches | [Issue #20](https://github.com/camaraproject/DeviceLocation/issues/20), [PR #31](https://github.com/camaraproject/DeviceLocation/pull/31)
                                                                    - Feedback from Orange to make `matchRate` optional | - `matchRate` shifted to optional
                                                                    - Let's see in future how we accommodate this attribute with future research (0-100; low, medium, high)

                                                                    - **Team OK with the change** | +| Polymorphic Area | [Issue #26](https://github.com/camaraproject/DeviceLocation/issues/26), [PR #29](https://github.com/camaraproject/DeviceLocation/pull/29)
                                                                    - New polymorphic model proposed. Only current `type = Circle` added
                                                                    - Prepared for new types | - Add Elevation? Bring a clear UC and open another issue. Issue is to get the information from the network
                                                                    - New types to be proposed, Telefónica to add Postcode, Orange to add polygon

                                                                    - **Team OK with the change** | +| Path rename | [Issue #30](https://github.com/camaraproject/DeviceLocation/issues/30), [PR #35](https://github.com/camaraproject/DeviceLocation/pull/35)
                                                                    - Proposal to rename path from `/verify` to `/verifications`, to align with guidelines
                                                                    - Feedback from Orange and Telefónica | - **Team OK with the change** | +| Multiple devices per request | [Issue #32](https://github.com/camaraproject/DeviceLocation/issues/32), [PR #33](https://github.com/camaraproject/DeviceLocation/pull/33)
                                                                    - Proposal to enable the location verification for multiple devices in one call.
                                                                    - Feedback from Telefónica, Orange | - Discussion in progress in DT
                                                                    - To be check if it is a bulk of 'autonomous' request or one business request with several UE
                                                                    - Need a bulk mechanism -> This is point to raise to Commonalities

                                                                    - **Keep it open for further discussion** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                                                                    - Mentioned previously but new issue
                                                                    - Feedback from Telefónica | - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered

                                                                    - **Keep in open for further discussion** | +| WoW: PRs to main | - It was agreed in Commonalities to keep the latest changes in `main` branch, even if it is no a stable version
                                                                    | - Proposal to merge current agreed PRs into `dev-0.2.0` branch, and then merge branch to `main` as version 0.2.0-wip
                                                                    - Any pending PR to branch `dev-0.2.0` to be moved to `main`
                                                                    - New PRs to be made to `main`

                                                                    - **@jlurien to merge the PR for agreed today to main**, then we can add PR to main. | + + +## AOB + +* DT is currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. +

                                                                    + +* Rafal raised the point about release management: + - 0.1 was released for MWC + - Right now we working on 0.2 + - We need to have an agreement around all API. +

                                                                    + +* Joachim Dahlgren asked for device location (not check). + + - Tuan Tran (Broadpeak) supports the UC + - This is in the scope of this projet + - We probably need to have different endpoint, scope, etc… + - We need an issue to discuss. + - Sensitive from privacy but very relevant with B2B +

                                                                    + +* Shuting asking about future roadmap on this API as today is only Device Location check + - Team indicated that the API will evolve in future with new capabilities +

                                                                    + +* **Next call is on March 28th.** \ No newline at end of file diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28.md new file mode 100644 index 0000000000000000000000000000000000000000..d9f4c0091757ed2ace53d0515703db0dfc042913 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-03-28.md @@ -0,0 +1,54 @@ +# CAMARA DeviceLocation meeting - 2023-03-28 + +*March 28th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Shuting Qing (Huawei) +* Shyamal Patabendige () +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - **Keep waiting until proposal is merged in QoD** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                                                                    - Some feedback by Orange and Telefónica
                                                                    - Some pending comments: Add DELETE and GET, support for susbcription termination due to consent removal (new event?)
                                                                    - Need alignment & feedback with other API (topic raised in Commonalities) | - Good progress in Commonalities
                                                                    - Not far from the work done in Device location

                                                                    - **Wait for outcome in Commonalities** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                                                                    - Feedback from Telefónica
                                                                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                                                                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated | - Wait for clear requirement to complete model

                                                                    - **Call for uses cases from the team, in particular for fresh information** | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39)
                                                                    - Proposal by TEF to add Postal Codes as new type of area
                                                                    - No feedback so far | - Discussion on the model, as other code could be used (like INSEE code in France)
                                                                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.

                                                                    - **Orange will provide information for France based on INSEE code** | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40)
                                                                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                                                                    - Proposal by Ericsson, feedback by DT and TEF | - Joachim: in our product we combine Device status & Device location.
                                                                    - The use case is interesting. Get more details from Product teams
                                                                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account.

                                                                    - **Ludovic will raise an issue in Commonalities about "multiple endpoint API" vs "multiple API"** | + + +## AOB + +* Question from Shuting about architecture + - **Should be asked to Commonalities** + +* In last meeting, DT mentioned to be currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. + - **DT dev on NEF on hold** +

                                                                    + +* In last meeting, Rafal raised the point about release management: + - 0.1 was released for MWC + - Right now we working on 0.2 + - We need to have an agreement around all API. + - Discussion on versioning. Proposal to change version each time we implement new code (each time we merge). DT mentioned that a Governance group is set up also to work on this topic, as right now is up to each sub projects. + - **We will decide on version update before merging new functionality.** +

                                                                    + + +* **Next call is on April 11th.** \ No newline at end of file diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11.md new file mode 100644 index 0000000000000000000000000000000000000000..c5ec6694e242419ac3bf3c1abc000f6cd0ba15c2 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-11.md @@ -0,0 +1,41 @@ +# CAMARA DeviceLocation meeting - 2023-04-11 + +*April 11th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Joachim Dahlgren (Ericsson) +* José Luis Urien (Telefónica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - **Keep waiting until proposal is merged in QoD** (no progress in the last 2 weeks, as QoD was cancelled) | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #27](https://github.com/camaraproject/DeviceLocation/pull/27)
                                                                    - Some feedback by Orange and Telefónica
                                                                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                                                                    - Good progress in Commonalities
                                                                    - Not far from the work done in Device location | - **Wait for outcome in Commonalities** (meeting planned April 12th with Akos & Pedro in order to close last comments - @Ludovic: hope to be able to make a proposal once validated by commonalities to device location) | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                                                                    - Feedback from Telefónica
                                                                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                                                                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                                                                    - Wait for clear requirement to complete model | - **Call for uses cases from the team, in particular for fresh information** (Need to figure out how it should work (DT) - Discussion also in Telefonica group)| +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                                                                    - Proposal by TEF to add Postal Codes as new type of area
                                                                    - Discussion on the model, as other code could be used (like INSEE code in France)
                                                                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                                                                    - Document that Circle is always supported | - No additional requirement from Orange on INSEE code used in France
                                                                    - **New PR proposed by Telefonica.** OK from Ludovic (Orange), Akos will take a look for DT | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                                                                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                                                                    - Proposal by Ericsson, feedback by DT and TEF
                                                                    - The use case is interesting. Get more details from Product teams
                                                                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF |

                                                                    - **Wait for more feedback from Commonalities**, and uses cases from Product teams | + + +## AOB + +* In last meeting, DT mentioned to be currently working on an implementation against the NEF + - To add implemenation code, we may need a new subproject per provider implementaion (PI)as QoD does. + - **DT dev on NEF on hold. Bring topic back if status changes** +

                                                                    + +* Rafal: need to clean some branches already merged. **@José will do.** +

                                                                    + +* **Next call is on April 25th.** \ No newline at end of file diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25.md new file mode 100644 index 0000000000000000000000000000000000000000..df4fe7136e35a83a081b66b4143252f9c01c7bbc --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-04-25.md @@ -0,0 +1,48 @@ +# CAMARA DeviceLocation meeting - 2023-04-25 + +*April 25th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Asad Imran Aslam (Etisalat) +* Hacene Sali (Etisalat) +* Jamal Sahyoun (Etisalat ) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Ludovic Robert (Orange) +* Prashant Sidana (Etisalat) +* Rafal Artych (DT) +* Ravi Shekhar () +* Shuting Qing (Huawei) +* Syed Iqbal Hussain (Etisalat) +* Tarek Abu-Shaban (Etisalat) +* Toshi Wakayama (KDDI) +* Tuan Tran (Broadpeak) +* Wisam S Salim Najim () + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business, review some topics raised in last meeting + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - QoD finally [merged changes, renaming `ueId` to `device`](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml)
                                                                    - Wait for agreement on IP description
                                                                    - **@jlurien will make a PR for this** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49)
                                                                    - Some feedback by Orange and Telefónica
                                                                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                                                                    - New PR proposed to `main` branch by @maxl2287 (DT), as previous one [#27](https://github.com/camaraproject/DeviceLocation/pull/27) was closed | - Some agreement reached in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156)
                                                                    - Still pending question about location
                                                                    - **PR once agreed (Max or Ludovic)** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                                                                    - Feedback from Telefónica
                                                                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                                                                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                                                                    - Wait for clear requirement to complete model | - Last days for the comments for #34
                                                                    - **@Akos will then make the PR** | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                                                                    - Proposal by TEF to add Postal Codes as new type of area
                                                                    - Discussion on the model, as other code could be used (like INSEE code in France)
                                                                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                                                                    - No additional requirement from Orange on INSEE code used in France |
                                                                    - Alignment on country code terminology (from Akos review) - **@jlurien will update the PR**
                                                                    - José reminds the business rational for adding postal code. All implementation must support circle area. All other area support is optional | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                                                                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                                                                    - Proposal by Ericsson, feedback by DT and TEF
                                                                    - The use case is interesting. Get more details from Product teams
                                                                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF and DT | - One or 2 APIs? Issue still open in Commonalities. From Telefonica & Orange preference to have 2 APIs on this UC to clearly separate check location from getting location. José rational for 2 APIs is to simplify release management. Joachim explained that from Ericsson they have separated in 2 APIs for security reason & distinct UC.
                                                                    - **Get DT feedback on this specific API** if comfortable with 1 or 2 APIs.
                                                                    - **@Ludovic can do a first PR for that once DT provide feedback**. We can have 2 yaml in API_definitions. Current yaml for location check need to be slightly revisited (naming, example, scope) | + + +## AOB + +* [PR #46](https://github.com/camaraproject/DeviceLocation/pull/46), related to [Issue #45](https://github.com/camaraproject/DeviceLocation/issues/45), merged and issue closed. + +* **Next call is on May 9th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09.md new file mode 100644 index 0000000000000000000000000000000000000000..b6488745d856abde70e77c46bcc664ff1dd9d37f --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-09.md @@ -0,0 +1,77 @@ +# CAMARA DeviceLocation meeting - 2023-05-09 + +*May 9th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Ludovic Robert (Orange) +* Mohammad Sahid Khan () +* Prashant Sidana (Etisalat) +* Tarek Abu-Shaban (Etisalat) +* Shyamal Patabendige () +* Udaka Kappagoda (Axiata Group) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Discussion + +| Agenda Item | Description | Discussion & Action Points | +| ----------- | ----------- | ------------ | +| Alignment with guidelines | [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12). We must adapt errors and properties to guidelines
                                                                    - Waiting for new model for `ueId`/`device` to be consolidated in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) WG. Expected for next weeks | - QoD finally [merged changes, renaming `ueId` to `device`](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml)
                                                                    - Wait for agreement on IP description. Still not resolved
                                                                    - **@jlurien will make a PR for this** | +| Subscription for Location Area | [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49)
                                                                    - Some feedback by Orange and Telefónica
                                                                    - Some pending comments: Add DELETE and GET, support for subscription termination due to consent removal (new event?)
                                                                    - New PR proposed to `main` branch by @maxl2287 (DT), as previous one [#27](https://github.com/camaraproject/DeviceLocation/pull/27) was closed | - Good review discussion in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156), May 4th,2023
                                                                    - Ludovic updated the guidelines accordingly. Now waiting for the merge in Commonalities
                                                                    - **PR once agreed (Ludovic)** | +| Add `maxAge` | [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34)
                                                                    - Feedback from Telefónica
                                                                    - LastLocationTime makes sense for B2B UB but team agreed that privacy constraint need to be considered
                                                                    - Also proposed as [Issue #42](https://github.com/camaraproject/DeviceLocation/issues/42), so closed as duplicated
                                                                    - Wait for clear requirement to complete model | - New [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) by @hbujakow (DT)
                                                                    - Same request than the one raised some time ago by Udaka Kappagoda
                                                                    - We need to provide explanation how the parameters needs to work
                                                                    - Documentation integration in OAS will be tracked in another PR
                                                                    - Let's wait to get review for this PR specifically | +| Postal Code Area | [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47)
                                                                    - Proposal by TEF to add Postal Codes as new type of area
                                                                    - Discussion on the model, as other code could be used (like INSEE code in France)
                                                                    - Model could accommodate to have several type of code, but our polymorphic model also allow us to be precise.
                                                                    - No additional requirement from Orange on INSEE code used in France
                                                                    - José reminds the business rational for adding postal code. All implementation must support circle area. All other area support is optional |
                                                                    - Alignment on country code terminology (from Akos review) - **@jlurien will update the PR**
                                                                    - Some new comments on both issue and PR by @RogerJL. TEF keeps the PR on hold until better clarification on how to support partial implementations. Issue about the adoption because need support for other Telco. Probably we need to keep only the Circle right now. | +| Provide location | [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [Commonalities Issue #178](https://github.com/camaraproject/WorkingGroups/issues/178)
                                                                    - Also new [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related
                                                                    - Proposal by Ericsson, feedback by DT and TEF
                                                                    - The use case is interesting. Get more details from Product teams
                                                                    - We agree that is a specific endpoint - discussion about adding it to the current API or have a separate API. Version management should be taken into account. Raised an issue in Commonalities about "multiple endpoint API" vs "multiple API - Feedback from TEF and DT | - Akos (DT) - ok for this API to have 2 distinct API.
                                                                    - **@Ludovic Ludovic will craft the swagger (not managing the subscription).** | + + +## AOB + +* [Issue #51](https://github.com/camaraproject/DeviceLocation/issues/51). Should we move parts of the schema shared by several projects to a common schema, such as `UeId`/`device`. Do we open an issue in Commonalities? + - We keep for now but the swagger must still be self-contained + - For ueId specifically we need always to be sync with other project. + - Have a common data dictionary will be definitely helpful but CAMARA is not yet at this stage +

                                                                    + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. **@Jose to open poll** +

                                                                    + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + - **@José will make it but after subscription is closed (and implemented)** +

                                                                    + +## Other questions during meeting + +* Question about checking CAMARA API compliance ? + - There is no formal certification process right now --> nobody will check the code + - CAMARA is about the interface not the code to provide it --> Implementation has to align on the swagger definition. + - Example of issue on compliance: how to have a common behavior for MatchRate compute - there will be interpretation by implementation. + - Good topic for discussion in Commonalities --> Need an issue. +

                                                                    + +* Comment about Partial answer + - Partial means the location match is no complete - but there will not additional response. This is not related to HTTP code 206. +

                                                                    + +* Discussion about event subscription + - Geofencing probably will be in Check Location + - But we can imagine other subscription to get directly location (every 30 minutes for example). In this case in will be the Get location API. Right now we do not have requested for this later. +

                                                                    + +* Question about authorization + - Several ways are defined but will be depending on local regulations + - Will be discussed case per case between consumer and provider + - This is beyond scope of this team +

                                                                    + +* **Next call is on May 23th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23.md new file mode 100644 index 0000000000000000000000000000000000000000..d53d51d3dfda3a2a9a29b2ed822c2a10d793d28b --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-05-23.md @@ -0,0 +1,103 @@ +# CAMARA DeviceLocation meeting - 2023-05-23 + +*May 23rd, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Amit Ahuja (Etisalat) +* Hacene Sali (Etisalat) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefónica) +* Mohammad Sahid Khan () +* Rafal Artych (DT) +* Ravi Shekhar (ravishek) +* Syed Iqbal Hussain +* Tuan Tran (Broadpeak) +* 若山 敏康 () + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12) + +* New model for `ueId`/`device` defined in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand), including new model for IPv4Address. Already merged + +* **@jlurien will make a PR for this** Still pending + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + +* Discussed in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156) + - Ludovic updated the guidelines accordingly. Now waiting for the merge in Commonalities, pending on discussion for Guidelines versioning. + +* **PR once agreed (Ludovic)** -> Pending, Ludovic updated by email that he's ok with versioning proposal. + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Also [Issue #43](https://github.com/camaraproject/DeviceLocation/issues/43) may be related -> **@ukkaps to clarify** + +* Agreed to have a separate API from the current one + - Proposal to move current one to a new basePath, e.g. `device-location-verification`, and leave `device-location` to this new one + - **@jlurien to open issue to discuss new name** + +* Review PR by Ludovic + - Discussion about modelling endpoint as POST vs GET in [Commonalities Issue #212](https://github.com/camaraproject/WorkingGroups/issues/212) + - Seems there is consensus about using POST for use cases like this one + - Opinions, further comments on the PR? + - **@Ludovic Ludovic will modify the spec** | + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **@all, please provide comments to PR** + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** -> Pending + +### Units for radius + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. + +* **@Jose to open new issue** + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF keeps the PR on hold + +## AOB + +* Some questions about general topics of CAMARA, not directly related to Device Location. Pointing to the right place to raise that questions. + +* DT ask for time planning for new Release. Agreed to open an issue with tentative scope and roadmap, as they did in QoD. **AP on @jlurien** + +* Joachim comments about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - Current proposal is not clear about that + - **Joachim to open issue** + +

                                                                    + +**Next call is on June 6th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06.md new file mode 100644 index 0000000000000000000000000000000000000000..8eafc18fe029c3331a024c2b4c43477f2d1427d5 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-06.md @@ -0,0 +1,135 @@ +# CAMARA DeviceLocation meeting - 2023-06-06 + +*June 6th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Asad Imran Aslam +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Ravi Shekar +* Sébastien Synold (Intersec) +* Shyamal Patabendige +* Toshi Wakayama (KDDI) +* Udaka Kappagoda (Axiata) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introduction to new members: Sébastien & Cetin +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15), related to [Issue #12](https://github.com/camaraproject/DeviceLocation/issues/12) + +* New model for `ueId`/`device` defined in [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand), including new model for IPv4Address. + +* New PR #61 [https://github.com/camaraproject/DeviceLocation/pull/61]. Reviewed by Orange +* **Merge planned June 7th EOB if no blocking comment** + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + +* Discussed in [Commonalities](https://github.com/camaraproject/WorkingGroups/issues/156) + - New model now consolidated in Guidelines. + - New [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/155) with a similar alignment to guidelines. It could be taken as example. + +* [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) by @maxl2287 (DT) needs to be adapted. * **DT will continue the crafting work** + +* Need discussion if Geo fence should be separated from check location operation as distinct model/business case could be provided. + - **Ludovic will create an issue to capture team feedback.** + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Agreed to have a separate API from the current one + - Proposal to move current one to a new basePath, e.g. `device-location-verification`, and leave `device-location` to this new one + - Issue [#59](https://github.com/camaraproject/DeviceLocation/issues/59). **To discuss during meeting** + +* Review PR by Ludovic + - Discussion about modelling endpoint as POST vs GET in [Commonalities Issue #212](https://github.com/camaraproject/WorkingGroups/issues/212) + - Seems there is consensus about using POST for use cases like this one + - Some comments and fixes in PR. + - Discussion in meeting about link with consent in particular when the location requested is for IoT - there is an Identity & Consent Management project where discussion occurs + +* **Merge planned June 7th EOB if no blocking comment.** + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **@all, please provide comments to PR** + - Need additional work to be completed as it is not 100% clear + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** +* **@Ludovic will make for the 'raw' location API** + +### Units for radius + +* [Issue #52](https://github.com/camaraproject/DeviceLocation/issues/52). Review doc/guidelines about units + - OK for doc enhancement + - Need to check if we are using meter or kilometer. + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discuss during meeting: Depending on the back end - glmc (meter accuracy) or nef - the accuracy is very different + +* **Ask for team to provide comments in issue** + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No comments so far + - Discuss during meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider + +* **Ask for team to provide comments in issue** + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in June featuring + - For check location: + - Rename location to location-verification (issue 59) + - Align device model (PR 61) + - Add documentation in the OAS + - For raw location: + - Provide v0.1 + - With documentation integrated in the OAS + - Release in August + - Adding location subscription/notification for checking location + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF keeps the PR on hold. + +* **TEF will move discussion to business track in GSMA (@Jorge)** + +## AOB + + +

                                                                    + +**Next call is on June 20th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20.md new file mode 100644 index 0000000000000000000000000000000000000000..61de824a0ec56e66d75ba473a55540f6ac721a19 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-06-20.md @@ -0,0 +1,140 @@ +# CAMARA DeviceLocation meeting - 2023-06-20 + +*June 20th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Alignment with guidelines + +* [Issue #15](https://github.com/camaraproject/DeviceLocation/issues/15) closed. +* [PR #61](https://github.com/camaraproject/DeviceLocation/pull/61) merged. + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + - To be aligned with Commonalities + - **DT will continue the crafting work** + +* [Issue #64](https://github.com/camaraproject/DeviceLocation/issues/64): Discussion if Geo fence should be separated from check location operation as distinct model/business case could be provided. + - **Team Decision**: We will have 2 APIS - Ludovic will comment issue & close it. + - Current Device location verification will stay only with one operation + - PR #49 should be close + - Need a discussion about the name + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Agreed to have a separate API from the current one + - [Issue #59](https://github.com/camaraproject/DeviceLocation/issues/59), [PR #66](https://github.com/camaraproject/DeviceLocation/pull/66) + - `device-location-verification` or `location-verification`: **Team Decision**: remove device prefix + +* Review PR by Ludovic + - **Team Decision**: need to switch to meter, related to [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discussion on age of location: + - Depends on the UC. If we do not provide age of location we need to have a global rule about retrieval delay + +* **Team Decision**: Regarding the date related parameters + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + +* Documentation will be handled in a second PR for raw location + +* Another API could be to have a history API but data are not obviously available from network. If needed, it is a separate use case. + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Some comments on the issue, no comments on PR + +* **Team Decision** Regarding the date related parameters: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) will be aligned. @José will comment +* @Ludovic will align raw location API + + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* **@José will make it but after subscription is closed (and implemented)** -> Pending +* **@Ludovic will make for the 'raw' location API**, separate PR after [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +### Units for radius + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Discuss during meeting: Depending on the back end - glmc (meter accuracy) or nef - the accuracy is very different + +* **Team decision**: Move to meters + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No comments so far + - Discuss during meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider + +* **Ask for team to provide comments in issue** + - Need to check how current system manage when the accuracy is to small - always False? + - Need additional discussion + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in June featuring + - For check location: + - Rename location to location-verification (issue 59) -> PR + - ~~Align device model (PR 61)~~ + - Add documentation in the OAS -> Pending PR + - For raw location: + - Provide v0.1 + - With documentation integrated in the OAS + - Release in August + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* TEF has moved discussion to business track in GSMA. Any update? + - Not yet, @Jorge provides update on business track. + +## AOB + + +

                                                                    + +**Next call is on July 4th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04.md new file mode 100644 index 0000000000000000000000000000000000000000..ee528f666fae71282cf081eabe90667e4c9dac65 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-04.md @@ -0,0 +1,145 @@ +# CAMARA DeviceLocation meeting - 2023-07-04 + +*July 4th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Ravi Shekhar () +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #49](https://github.com/camaraproject/DeviceLocation/pull/49) + - PR #49 should be close, new PR to be created + - **DT will open new PR soon** + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - Orange preference for `location-verification-subscription` + - Keep open to get more opinions + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + +* Review PR by @Orange: + - Switched to meters + - Added `maxAge` (optional) to request + - Added `lastLocationTime` (required) to response + - Documentation will be handled in a second PR for raw location + +* Almost ready - Ludovic will integrate José requests this week +* Align Area model with Location verification with allOf + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Agreed: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* Comments in [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53). It must be rebased, or close this and new PR + - ** @DT will discuss with the team how to process (rebase or new PR) ** +* Applied to [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + + +### Consolidate documentation into spec + +* Adopt [decision in Commonalities](https://github.com/camaraproject/WorkingGroups/issues/164) about keeping API documentation as part of the spec + +* New [PR #71](https://github.com/camaraproject/DeviceLocation/pull/71), + - **ready to be merged** + + +### Units for radius + +* [Issue #60](https://github.com/camaraproject/DeviceLocation/issues/60) + - Decided to move to meters. + - Pending new PR -> @TEF will do it, just converting to meters + +* Decide on new limits. Now, they are 2km to 200 km + - Discussion to set minimum to 1 km + - Privacy needs to be considered if we are too precise. + - Probably better for now to keep 2 km. + - Question from Joachim Dahlgren about correlation between precision vs consent required + - Question from Cetin about the max - Do we really need to set to 200 km explicitly + - We can remove it probably? + - ** AP: Open an Issue to discuss this. ** + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No new comments + - From previous meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider, need to check how current system manage when the accuracy is to small - always False? + +* To be discussed during meeting. + - ** @TEF will provide examples about 'Partial' UC ** + - We need to align on the formula to calculate the 'matchRate' for PARTIAL answer + + +### Align Area to new model for inheritance vs polymorphism + +* [Issue #72](https://github.com/camaraproject/DeviceLocation/issues/72) + - ** @TEF will open new PR ** + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in July featuring + - For check location: + - ~~Rename location to location-verification (issue 59)~~ + - ~~Align device model (PR 61)~~ + - Add documentation in the OAS -> PR to be merged + - For raw location: + - Provide v0.1 -> PR to be merged + - With documentation integrated in the OAS -> Pending PR + - Release in August / September (depending on holidays): + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* New request from GSMA to add administrative code (like postal code) + - How we will manage case where implementation did not provide all location type?, Discovery?, Error? + +* **@TEF: add a new issue and close this one.** + + +## AOB + +* Add a file for summer presence (Ludovic will do) + +

                                                                    + +**Next call is on July 18th.** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18.md new file mode 100644 index 0000000000000000000000000000000000000000..6e12f6f2c916150943033d8bea2e19fa07f2f5b1 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-07-18.md @@ -0,0 +1,148 @@ +# CAMARA DeviceLocation meeting - 2023-07-18 + +*July 18th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Sébastien Synold (Intersec) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Subscription for Location Area + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Old PR #49 was close, new PR created + - Many comments, most resolved. Ongoing discussions in Commonalities may affect this PR. + - Probably better to **stick to current design** and then adjust later. + - DT team keeps the design aligned with Device Status API. + - Ludovic Robert will make a review of his previous comments to close resolved one + + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - Orange preference for `location-verification-subscription`, Ericsson preference for `geofencing` + - Joachim Dahlgren provided rational for geofencing instead of location-verification-subscription as we can have a second location subscription feature for geotracking. + - DT as owner of this API will consider this naming proposal and get back to the team (Akos Hunyadi) + - Looking for team feedback + + + +### New API to provide raw location + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Most comments resolved + - José Luis Urien Pinedo will make a final review + - Ludovic will work on the documentation only once PR#55 has been merged to avoid + + +### Add new parameter `maxAge` + +* [Issue #34](https://github.com/camaraproject/DeviceLocation/issues/34), [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53) + +* Agreed: + - `lastLocationTime` in the response mandatory + - `maxAge` will be optional in the request + - Add explicit information of maxAge about the fact that its concerns only the last location + - `maxAge` will be in second with a minimum of 60. + +* Comments in [PR #53](https://github.com/camaraproject/DeviceLocation/pull/53). It must be rebased, or close this and new PR + - ** @DT will discuss with the team how to process (rebase or new PR) ** -> José will check but the rebase has probably been already done +* Applied to [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + - No new comments + - From previous meeting: We need to provide a hint that the precision request is (definitely) too fine for API provider, need to check how current system manage when the accuracy is to small - always False? + +* To be discussed during meeting. + - ** @TEF will provide examples about 'Partial' UC ** -> Some internal discussions, José will post some material to illustrate the problem; + - We need to align on the formula to calculate the 'matchRate' for PARTIAL answer + + +### Roadmap for Release v0.2 + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. +* Our roadmap could be: + - Release in July featuring + - For check location: -> ready for 0.2 + - ~~Rename location to location-verification (issue 59)~~ + - ~~Align device model (PR 61)~~ + - ~~Add documentation in the OAS~~ + - For raw location: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - With documentation integrated in the OAS -> Pending PR + - Release in August / September (depending on holidays): + - Adding location subscription/notification for checking location + +* From roadmap perspective we are on track for API definition - for the documentation it could be probably delivered in July. + + +### Postal Code Area + +* [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39), [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) + +* Proposal by TEF to add Postal Codes as new type of area, lack of support from other partners about the business case + +* New request from GSMA to add administrative code (like postal code) + - How we will manage case where implementation did not provide all location type?, Discovery?, Error? + +* **@TEF: add a new issue and close this one.** -> Pending + +* Discussion on how to handle the 'diversity' of the 'geo' code that we can have in a given country. + +* How a developer will know the 'type' of area managed by a telco + - José mentioned discussion about TMF Catalog API (as operate API) - As a discovery feature. + - An error scenario must be defined in CAMARA if the area type requested is not supported by the telco + + +## Test Cases + +* New [Issue #80](https://github.com/camaraproject/DeviceLocation/issues/80) + +* Wait for other working group & commonalities agreement alignment + +* Discussion about use of Gherkin + specific implementation + - Gherkin file should (must?) be provided + - Specific language implementation file could be provided but as part of implementation contribution + + +## Accuracy Levels for Device Location APIs + +* New [Issue #78](https://github.com/camaraproject/DeviceLocation/issues/78) + - Discuss if we need this functionality + +* José/Ludovic not sure about the relevance of the problem with current technology as we're not able to provide 'fine-grain' location. + +* Joachim raised that if we have this capabilities to provide coarse vs fine we'll have a consent issue that cannot be at 'global' api level but dependent on the accuracy + + +## Summer 2023 presence + +* New [PR #75](https://github.com/camaraproject/DeviceLocation/pull/75) + - Only Ludovic added this presence + +* Keep Aug 1st - José will host. +* Skip Aug 15th …. except of someone volunteer to host it + + +

                                                                    + +**Next call is on August 1st** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01.md new file mode 100644 index 0000000000000000000000000000000000000000..05b05033af846547a0e9880c7fd9c3aaca1f710d --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-01.md @@ -0,0 +1,100 @@ +# CAMARA DeviceLocation meeting - 2023-08-01 + +*August 1st, 2023* + +## Attendees + +* Abhisek Das (Infosys) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (TEF) +* Javier Carro (TEF) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Rafal Artych (DT) +* Toshi Wakayama (KDDI) +* Tuan Tran (Broadpeak) + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Old PR #49 was close, new PR created + - Comments addressed, ready for final approval + +* [Issue #69](https://github.com/camaraproject/DeviceLocation/issues/69): Proposal for new name + - `geofencing` got consensus as name, PR updated, issue closed + + +### New API to provide raw location, v0.1-wip + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Reviewed, has 2 approvals. Ready to be merged + - Ludovic will work on the documentation only once PR#55 has been merged to avoid + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - Discussion during meeting. Issue to be updated: + - Akos commented that the ratio may not be enough and maybe we should add some text or rational. + - Cetin thinks that it makes sense to return a low percent since it is caused by a bad behaviour of the network. + - Telefónica agrees but raise the problem with Product team approach and how the quality of the product is perceived. + - We will see the possibility to split the partial values into different values as proposed by Jose and Akos. + +### Roadmap for Release v0.2 + +* New [Issue #84](https://github.com/camaraproject/DeviceLocation/issues/84) to unify naming for POST operations + - Current one: POST /verifications + POST /retrieve-location + - Decide on POST /verify-location + POST /retrieve-location, or simpler: POST /verify + POST /retrieve + - **Agreed to change paths to POST /verify + POST /retrieve** + +* We have to decide in Commonalities how to communicate roadmap for multiple API project. + +* Our roadmap could be: + - Release in August featuring + - For location-verification: -> ready for 0.2 + - For location: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - For geofencing: + - Provide v0.1 -> ready to be merged - documentation will be tackled in a separate PR + - Release in late August / September (depending on holidays): + + +### Postal Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track, closing old [Issue #39](https://github.com/camaraproject/DeviceLocation/issues/39). [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) to be closed when new one is created. + +* Some initial comments, we can start discussion but this requirement will be in the scope of future releases. + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco + +* Requirement to be covered by future releases, we keep discussion open in issue. + + +## Summer 2023 presence + +* Decided to skip Aug 15th + + +## AOB + +* Akos raises the Commonalities Issue regarding CloudEvents and how it will affect the Geofencing API. + - From Telefónica, another colleague is working on the issue and will update Commonalities in the next days. + +

                                                                    + +**Next call is on August 29th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29.md new file mode 100644 index 0000000000000000000000000000000000000000..bfd1fbbf9a7f022cdbbfcdc041fa64c8fbe1acff --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-08-29.md @@ -0,0 +1,86 @@ +# CAMARA DeviceLocation meeting - 2023-08-29 + +*August 29th, 2023* + +## Attendees + +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Jorge Garcia Hospital (TEF) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Vidhi Mehta (Comviva) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Location Retrieval, v0.1-wip (Get raw location) + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Official name to be location-retrieval + - Reviewed, has 2 approvals. Decided to merge! + - Ludovic will work on the documentation only once PR#55 has been merged + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Ludovic provided feedback on notification discussion in Commonalities, progress & plan: + - Have a specific swagger for generic notification + - Format for this dedicated notification swagger --> probably use Cloud Event structure + - Use of callbacks clause in the API swagger to describe API notification + - Issue API Design for "Resource-based subscription", [Commonalities Issue #44](https://github.com/camaraproject/Commonalities/issues/44) is the good place to follow progress + - Some comments still pending + - Probably for next meeting we can align Geofencing with commonalities + - Close to be merged as v0.1.0-wip, inline doc to be added later + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53) +* Next steps: + - Create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, if aligned with Commonalities + - Give a couple of weeks for final testing and comments + - Approve a release after next meeting + + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - Further discussion needed. Orange team will make a review. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) to be closed when new one is created. +* No new comments since last meeting, same questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. +* Discussion during the meeting: + - These questions could have a larger magnitude than this Device location API and should also infuse in Commonalities + - Adding Open Gateway product in the discussion could make sense as this OPGW could probably restrict a CAMARA API capability + - Discussion on the 'critical mass' to introduce API or API capability within one country. + + + +## AOB +N/A + +

                                                                    + +**Next call is on September 12th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12.md new file mode 100644 index 0000000000000000000000000000000000000000..43c1f7afd8f62e9a75d3e1c07aa6dc9111ce13f2 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-12.md @@ -0,0 +1,93 @@ +# CAMARA DeviceLocation meeting - 2023-09-12 + +*September 12th, 2023* + +## Attendees + +* Akos Hunyadi (DT) +* Fernando Prado Cabrillo (TEF) +* Javier Carro (TEF) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (TEF) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Location Retrieval, v0.1-wip (Get raw location) + +* [Issue #40](https://github.com/camaraproject/DeviceLocation/issues/40), [PR #55](https://github.com/camaraproject/DeviceLocation/pull/55) + - Merged but any comment are welcome + - Joachim: Maybe we should consider to send back other area than circle. +This is only in the response -> **@Joachim will raise an issue** + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Notification pattern is still in progress in Commonalities to accommodate use of [CloudEvents](https://github.com/camaraproject/Commonalities/pull/56) -> Once the model close in Commonalities should be quick to craft the API. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - PR still not merged, we should wait until Commonalities are approved. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + +* Joachim asked the question about consistence between the release name and the API name. + - Perhaps we can have a name for a family release + - Good topic to release in Commonalities -> **@Ludovic will raise an issue in Commonalities** + +### Behaviour when requesting too high precision + +* [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) about what is expected behaviour when requested accuracy is more restrictive that the one that network is able to satisfy. + +* New [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* Discussion during meeting: + - Ludovic provided comment on José document + - The first point is to be aligned on the matchRate formulae. + - Both TEF & Orange feedbacks are that most of the result will be false or partial but very few chance to get True result. + - The problem is more significant if we allow 'small' scope (minimum radius) + - Good to keep in open + - **@Ludovic will fix the comment - should be matchRate no maxRate** + - Joachim: other alternative will be to answer the True/False but also the location + - This is not easy for Privacy issue + - We have the 'other' API to trigger this. + - Javier look on Ludovic proposal: could have worst result but in same time current approach did not cover all the case. + - After discussion seems that the team direction is to work on the PARTIAL answer and differentiate depending on the situation (see José document UC 3 & 4 for example). The PARTIAL answer could be completed with additional information + - **Think about improving PARTIAL information for next version** + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + +* No new comments since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                                                                    + +**Next call is on September 26th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26.md new file mode 100644 index 0000000000000000000000000000000000000000..2425d766dca51b8af6e2078ea64a9feafc295ef3 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-09-26.md @@ -0,0 +1,104 @@ +# CAMARA DeviceLocation meeting - 2023-09-26 + +*September 26th, 2023* + +## Attendees + +* José Luis Urien (TEF) +* Nicholas Venezia (centillion.ai) +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgren (Ericsson) +* Akos Hunyadi (DT) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Jorge Garcia Hospital (TEF) +* Javier Carro Calador (TEF) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Notification pattern is still in progress in Commonalities to accommodate use of [CloudEvents](https://github.com/camaraproject/Commonalities/pull/56) -> Once the model close in Commonalities should be quick to craft the API. + - Discuss progress in commonalities but close to be merged + - José is OK and wait Pedro return to validate + - Shilpa validated + - Objective is to have the API ready for review for next meeting. + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Other possible areas other than circle + - Discuss which ones make sense: Polygon, Ellipse/EllipsoidArc, Areas including altitude? + - Positive feedback from Telefonica in particular for polygon in a first step. Orange shares this feedback for Polygon. + - José raised the point about multi-polygon + - Joachin mentionned used of GMLC + - **[question]** Question on how getting the altitude. + - **[action]** Check how the network how the polygon is described (set of points) and then we can craft the P/R to improve the API with this new feature. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [Draft PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, changing securitySchemes to openIdConnect. Waiting for resolution in Commonalities and Identity and Consent Management WGs. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Proposal to use date format, such as Release 2023-09, but no agreement so far. + - **[action]** José will check how this release management for a family is done within Edge API + - **[decision]** Without formal decision we will use the date & lead the path + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85), related to [Issue #58](https://github.com/camaraproject/DeviceLocation/issues/58) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* Discussion during previous meeting: + - Need to align on the matchRate formulae. + - Problem with current proposal is that result will be false or partial but very few chance to get True result. The problem is more significant if we allow small areas as input. + - After discussion seems that the team direction is to work on the PARTIAL answer and differentiate depending on the situation (see José document UC 3 & 4 for example). The PARTIAL answer could be completed with additional information + - **Think about improving PARTIAL information for next version** + - Joachim had an internal review of the document - we have to write a document to explain how the matchRate is calculated. + - Discussion on the consent but probably not difference between retrieval & verification. + - The problem we have here for Location Verification will be also very significant for future geofencing API. + - Probably we need to have more maturity on this with some real implementation + - Nicholas Venezia provides feedback on how the Device location API is used within a podcast app to provide targeted ad. Nicholas demonstrated utilisation of location data. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + - Javier shared a proposal on this topic. + - **[Question]** How to map postal code to geolocation/coordinate? + - depending on the country - could be provided by local regulations + - Javier will share the proposal in the GIT. + +* No new comments or progress since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                                                                    + +**Next call is on October 10th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10.md new file mode 100644 index 0000000000000000000000000000000000000000..952acef1de32fffb2359036647ad843017bf7305 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-10.md @@ -0,0 +1,114 @@ +# CAMARA DeviceLocation meeting - 2023-10-10 + +*October 10th, 2023* + +## Attendees + +* José Luis Urien (Telefonica) +* Foo Ming Hui (Singtel) +* Cetin Alpaycetin (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Rafal Artych (DT) +* Akos Hunyadi (DT) +* Sébastien Synold (Intersec) +* Ludovic Robert (Orange) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Javier Carro Calador (Telefonica) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - New model based on CloudEvents are now approved + - PR proposed by DT https://github.com/camaraproject/DeviceLocation/pull/98 before the meeting. + - Ludovic raised the point about the event granularity - José shared the point and also expected 2 event types. + - Akos questionned if we need maxRate in this API. + - Cetin explained that in Vodafone implementation the cell id is used as an input. This will need API consumer to 'know' the cell which is a 'technical' information. + - [action] PR#74 could be close and point to PR#98 + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Other possible areas other than circle + - Discuss which ones make sense: Polygon, Ellipse/EllipsoidArc, Areas including altitude? + - Some comments on issue: + - OK to add polygon? + - Others? + + - José provided a feedback about TS29.572 review + - Limit to max 15 points could be challenged + - [action] Need PR for adding polygon as it is obvious. + - Need additional thinking for other area type + - Ludovic: What about adding the cell id ? + - José: It could be a way to discover the cell id but perhaps we could have a dedicated endpoint. + - [action] Worth to open an issue for this and think about it. + - Joachim : Need to verify if telco are willing to share this information. José: Perhaps using an alias could be an alternative. + - Discussion to be continued. + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, changing securitySchemes to openIdConnect. Waiting for resolution in Commonalities and Identity and Consent Management WGs. + - Some approvals, can we merge? + - [Decision] Yes + - Joachim questionned about OIDC flows use-able. + - José/Ludovic answered that the proposal allow flexibilty by splitting the API yaml from the managed authorization for the API. This solution did not restriction authorization flow. In order to simplify adoption authorization flow must be constitent within one country + - [Action] : check for Device-location-retrieval and if not aligned to be tackled in next version. + +* Next steps: + - Then create v0.2-rc for location-verification, updating Changelog and Release notes. + - Add location-retrieval v0.1.0-wip + - Add geofencing v0.1.0-wip, after discussion in Commonalities is closed. + - geofencing has to be aligned with CloudEvents + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Proposal to use date format, such as Release 2023-09, but no agreement so far. + - EdgeCloud API using v1, v2 ... + - What name should we choose? + - [Decision] Let's wait for next TSC outcome. + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* No new comments +* Need a better name for Partial (Javier will work on it) + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - Old [PR #47](https://github.com/camaraproject/DeviceLocation/pull/47) closed. + - Javier shared a proposal on this topic. + - **[Question]** How to map postal code to geolocation/coordinate? + - depending on the country - could be provided by local regulations + - [Action] Javier will share the proposal in the GIT. + +* No new comments or progress since last meeting, **no update or discussion during meeting**. Previous questions/doubts: + - How to handle the 'diversity' of the 'geo' code that we can have in a given country. + - How to discover what is implemented by each provider. + - Error scenario must be defined in CAMARA if the area type requested is not supported by the telco. + + +## AOB +N/A + +

                                                                    + +**Next call is on October 24th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24.md new file mode 100644 index 0000000000000000000000000000000000000000..48fb7ab8e684d02b608428fcc1b5eb753cc602ba --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-10-24.md @@ -0,0 +1,118 @@ +# CAMARA DeviceLocation meeting - 2023-10-24 + +*October 24th, 2023* + +## Attendees + +[x] José Luis Urien (Telefonica) +[] Foo Ming Hui (Singtel) +[x] Cetin Alpaycetin (Vodafone) +[x] Joachim Dahlgreen (Ericsson) +[x] Rafal Artych (DT) +[x] Akos Hunyadi (DT) +[] Sébastien Synold (Intersec) +[x] Ludovic Robert (Orange) +[x] Fernando Prado Cabrillo (Telefonica) +[] Jorge Garcia Hospital (Telefonica) +[] Javier Carro Calador (Telefonica) +[x] Ramesh Shanmugasundaram +[x] Amit Ajuha +[x] Parichaya Shrivastava + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + + +## Open issues and PRs + + +### Geofencing v0.1-wip (Subscription for Location Area) + +* [Issue #18](https://github.com/camaraproject/DeviceLocation/issues/18), [PR #74](https://github.com/camaraproject/DeviceLocation/pull/74) + - Review last comments in PR + - Good progress - few comments left: + * Basepath should be enum and not default - Issue in Commonalities raised by José + * Move to openId for security schema + * Adding data in termination event + * Safer to include the information in the event body + + - Ludovic will update the commonalities on subscription/event after first usage in Device location, Device status & Sim Swap. + - Joachim raised the point about adding other area type --> will be done in future PR. + + +### New: Location retrieval - Allow additional area types in the response + +* [Issue #94](https://github.com/camaraproject/DeviceLocation/issues/94) + - Review last [PR #100](https://github.com/camaraproject/DeviceLocation/pull/100) adding polygon + - PR ready: + - limit to 15: OK for the team. + - [action] for Ludovic: + - Add precision about close shape in the documentation for polygon. This is not required to provide twiwe a point. + - Align with security schema (discussed in TSC but not finalized in the documentation) + - Align with basepath with an enum + + +### Roadmap to Release v0.2 + +* The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + +* Align the Device Location API with the security schema as described in Unify specification of `securitySchemes`, `security` and scopes, [Commonalities Issue #53](https://github.com/camaraproject/Commonalities/issues/53), [PR #57](https://github.com/camaraproject/Commonalities/pull/57) + - [PR #95](https://github.com/camaraproject/DeviceLocation/pull/95) for location-verification, already merged after discussion in TSC. + - Apply the same to location-retrieval and geofencing? + +* Naming of the Release + - Issue opened in [Commonalities Issue #60](https://github.com/camaraproject/Commonalities/issues/60) + - Review discussion in TSC and agree on a name + - Discussed in TSC: + - DT will write a proposal on managing the proposal both for the API yaml(s) and family + - Have a global release for all CAMARA API for MWC 2024 + + +* Release content: + - location-verification v0.2-rc + - location-retrieval v0.1.0-wip + - geofencing v0.1.0-wip + - Changelog and Release notes. + +Points discussed: +* All this yaml will be under **0.2** family +* [action] For location-verification, José will fix the basepath with enum instead of default. + + +### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + +## AOB + +**Discussion on 3-legs pattern** raised by Joachim + * What is the third leg ? Is it always the flow going to the responsible 'party' for 'consent' grant? + * Let's take the example of a connected dog collar - The 'consent' should be provided by the user of the application tracking the dog. + * This management of the responsible 'party' for 'consent' grant is managed in the Authorization Server (AS). The AS for a given request for a device, a purpose and a data clain, compute the legal base and 'execute' it. Depending on the legal base there is not always a interaction with the responsible 'party' for 'consent' grant. + * Do we need to explictly provides in the request the device identifier as we can have it in the 'first leg'? + * This is relevant for some UC but we have UC where the Device A could trigger location request for another device. + * We mentioned the documentation provided in Identity&Consent management WG. + * We probably need to mention/point/refer this documentation in device location family API - We need to discuss how this information could be provided. + * The discussion will continue in following calls and depending on the work progress in Identity&Consent management WG. + +José will share the information to join the **Slack** + +

                                                                    + +**Next call is on November 7th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07.md new file mode 100644 index 0000000000000000000000000000000000000000..65cda0ea474c2537936fa5ff1cc07cd26c884a27 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-07.md @@ -0,0 +1,93 @@ +# CAMARA DeviceLocation meeting - 2023-11-07 + +*November 7th, 2023* + +## Attendees + +- José Luis Urien (TEF) +- Joachim Dahlgreen (Ericsson) +- Jayant Nagaraj (Shabodi) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Nicholas Venezia (Centillion) +- Fernando Prado Cabrillo (TEF) +- Rafal Artych (DT) +- Ludovic Robert (Orange) +- Jorge Garcia Hospital (TEF) +- Javier Carro Calador (TEF) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - The proposed process for a version is to have a version x.y-wip then x.y-rc and then finally released as x.y. This pattern is used in QoD. + - Doc updated + - basePath fixed in URL + - Examples updated + - Decide what to do with IPV6 pattern + - José triggered an isue in QoD to discuss IPV6 format and then will align. José suggests to remove pattern if not fully correct (As of now this pattern did nort work for some subnet mask definition) + - We are waiting for QoD outcome on this point. + - Joachim suggested to raise an issue in Commonalitiesa we have to align this in every API as this is a generic topic + - Akos explained that we can merge even as rc because it is valid to still update rc + +* Review new README and CHANGELOG + - [PR #106](https://github.com/camaraproject/DeviceLocation/pull/106) + - Inspired by model in QoD + - *Links will work after branch for Release-0.2.0 is created* + - Discussion on versinning name and use of wip & rc suffix + - Location-Verification is in Alpha version + - Discussion if location-retrieval should be also in Alpha version. + - Geofencing shouldn't stay in pre-Alpha as there are not open issue (_note that pre-alpha is not a defined state_). Joachim explained that for him if it's wip then we do no code it (which is a fair argument to move geofencing to rc) + +* Release content: + - location-verification v0.2-rc + - location-retrieval v0.1.0-wip -> Do we keep -wip? + - We should create also a rc and align with current work for location verification. + - Decision: should be promoted to v0.1-rc + - **Ludovic (for Orange) will create a PR** + - geofencing v0.1.0-wip -> Do we keep -wip? + - Decision: should be promoted v0.1-rc + - **Max (for DT) will create a PR** + - Changelog and Release notes. + - **José asked the team to take a close look on PR#106 as this is what the external public will see.** + + - Akos suggests to create an issue for tracking and the 3 PR will refer this one. + +### New Issues + +* security and scopes for the Device Location API [#105](https://github.com/camaraproject/DeviceLocation/issues/105) + * --> Probably good to rout to identity & consent management project + +### Open discussions + +#### Behaviour when requesting too high precision + +_Not enough time to discuss_ + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + +## AOB + + +

                                                                    + +**Next call is on November 21th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21.md new file mode 100644 index 0000000000000000000000000000000000000000..c75f0836659656b8ce8d6fb3c2d0c595aedbbb54 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-11-21.md @@ -0,0 +1,114 @@ +# CAMARA DeviceLocation meeting - 2023-11-21 + +*November 21st, 2023* + +## Attendees + +- José Luis Urien (TEF) +- Javier Carro Calador (TEF) +- Nicholas Venezia (Centillion) +- Ben Thomas (Vodafone) +- Foo Ming Hui (SingTel) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Jorge Garcia Hospital (TEF) +- Ludovic Robert (Orange) +- Fernando Prado Cabrillo (TEF) +- Sébastien Synold (Intersec) +- Rafal Artych (DT) +- Surajj Jaggernath (Vodacom) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - Point about Ipv6 still open in QoD (will be valid for all three APIs) + - Description comment from Cetin to be considered + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - Error: Status & Code are 'normative' - message are open to modification by implementation + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - Rafal proposed to align Notification source example list accordingly to the guidelines + +We're still in line to release before the end of the year. + - Resolve pending comments and merge current PRs as -rc + - Open testing and feedback period for RC versions + + We need also to align with the new working group about release management + + First training Nov 21th + Rafal, Ludovic and José will attend + + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + +### Review other Issues and PRs + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Discussed during meeting + - To be discussed in Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + + - The team needs to be involved in this work + - Agreed to use Gherkin must we should have an alignement on the formal aspect + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - To be aligned with ongoing discussion and [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/237) + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + +* [Geofencing API - Semantic error](https://github.com/camaraproject/DeviceLocation/issues/109) + - Solved & closed + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Discuss during meeting + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + +* New comments in Github from Joachim + * 3 scenarios illustrated + * [action] Review this comment. + +**[Decision]** Proposal is to use the formula defined in the Word document by Telefonica Team. + API documentation will be updated --> Add a document and have a link in each yaml to refer it. Telefonica will craft this document. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + + - Question from José if we need to keep this function in a same API or in a distinct one. + - This feature is not top priority right now but will be discused next year. + +Question about API certification from Ludovic + - Location retrieval is a good candidate + - topic links to the Test definition + - Let's wait for test definition outcomes and then we will assess use of this asset for certification purpose. + +## AOB + + +

                                                                    + +**Next call is on December 5th** + José will be off - Fernando & Ludovic will host the call. diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05.md new file mode 100644 index 0000000000000000000000000000000000000000..74d1c7b0821f7b356348748fbe43dfd60c5ce50e --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-05.md @@ -0,0 +1,113 @@ +# CAMARA DeviceLocation meeting - 2023-12-5 + +*December 5th, 2023* + +## Attendees + + +- Ludovic Robert (Orange) +- Fernando Prado Cabrillo (TEF) +- Foo Ming Hui (SingTel) +- Cetin Alpaycetin (Vodafone) +- Akos Hunyadi (DT) +- Javier Carro (TEF) +- Rafal Artych (DT) +- Joachim Dahlgreen (Ericsson) +- Sönke Peters (Vodafone) +- Surajj Jaggernath (Vodacom) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs + * No new issue for last 2 weeks + * Cleaning for old issues +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/104) + - Point about Ipv6 solved + - Description comments from Cetin considered + - Precision on date time accordingly to the commonalities guidelines + - MERGED during the meeting + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - Point about Ipv6 solved (complete alignment with verification device structure) + - Ready to review + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - Rafal aligned Notification source example list accordingly to the guidelines + - Alignment with IP v6 to be done. + - Akos will align ip addresses and device model as has been done with location retrieval and location verification + - Typo found in "expiresAt" subscription info. Akos will fix. + + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + - No new comment since last meeting + +### Review other Issues and PRs + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - No progress + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - Aligned with ongoing discussion and [PR in QoD](https://github.com/camaraproject/QualityOnDemand/pull/237) + - Done for Location retrieval & location verification + - To be done for geofencing + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Ludovic answered. + +* [Documentation Updated](https://github.com/camaraproject/DeviceLocation/issues/102) + - part of https://github.com/camaraproject/DeviceLocation/pull/104 + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - During previous meeting we agreed to use the formula defined in the Word document. + - Descriptions regarding partials and matchRate has been added in location-verification yaml + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + + +### Cleaning - issues closed +* [Does DeviceLocation itself really need to define all ways to identify a User equipment identifier](https://github.com/camaraproject/DeviceLocation/issues/51) - Tackled with https://github.com/camaraproject/DeviceLocation/issues/117 + +* [Include locationType as a request parameter](https://github.com/camaraproject/DeviceLocation/issues/43) - Request for Office/work location (most latched site/location in the day time) & Home location (most latched site/location in the night time). Managed in separate API request. + - Issue closed - Tackled with https://github.com/camaraproject/WorkingGroups/issues/336 + + [Accuracy Levels for Device Location APIs](https://github.com/camaraproject/DeviceLocation/issues/78) - nu update since July 31st José request for clarification to the issuer. + - Issue closed as there have been no updates in 3 months + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + + + +## AOB + + +

                                                                    + +**Next call is on December 19th** diff --git a/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19.md b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19.md new file mode 100644 index 0000000000000000000000000000000000000000..37f518c199523817a71b02a584869e01b341cc5c --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/2023/MoM-2023-12-19.md @@ -0,0 +1,117 @@ +# CAMARA DeviceLocation meeting - 2023-12-19 + +*December 19th, 2023* + +## Attendees +José Luis Urien Pinedo (Telefonica) +Ludovic Robert (Orange) +Surajj Jaggernath (Vodacom) +Cetin Alpaycetin (Vodafone) +Joachim Dahlgren (Ericsson) +Akos Hunyadi (DT) +Ravi Shekhar +Javier Carro Calabor (Telefonica) + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review Release Candidate v0.2 + +* Review latest comments in ongoing PRs for APIs, and decide if ready to be merged: + - [location-verification.yaml v0.2 Release Candidate](https://github.com/camaraproject/DeviceLocation/blob/main/code/API_definitions/location-verification.yaml) + - Already merged + - Minor fix merged: [Fix MaxAge type](https://github.com/camaraproject/DeviceLocation/pull/126) + - Any further comment/bug found? + - [location-retrieval.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/114) + - PR approved + - Merged + - [geofencing.yaml v0.1 Release Candidate](https://github.com/camaraproject/DeviceLocation/pull/116) + - PR approved + - Merged + +* Review latest comments in PR for README and CHANGELOG, and decide if ready to be merged: + - [Release Notes](https://github.com/camaraproject/DeviceLocation/pull/106) + - *Links will work after branch for Release-0.2.0 is created* + - No new comment since last meeting + - José will take a last look and merge this PR. + +### Review other Issues and PRs + +#### New + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - José tested locally for location verification + - José plans to do same for the other APIs + - No major issue identified (only warning). + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Relevant question for possible enhancement. To be discussed. + - José took a look on google API implementation and they have a new input parameter to let client decide if she/he decide to get an event at subscription time. This is relevant only for entered area event. + - We can introduce a `initialTriggerAreaEntered` boolean - if it is true then a notification is sent if the mobile is within the area. + - Akos said that we can send the notification in every case (not requiring this attribute) + - Joachim raises the point about how we can distinct the fact that the device was already in the area vs it just entered in for this first event. + - A combination with Location retrieval could be also documented. Ludovic says that it can work except if the device just entered at subscription time. + - **We need to open an issue to discuss** about the compute rule for geofencing area match. We solved this for device verification API (for `matchRate`) but here this is different as it is dynamic. + - Recommendation to continue the discussion on the issue. + +#### From previous meeting + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - No progress + - DT Team has provided comment + - TEF team will also provide comments + - Discussion should continue in Commonalities + +* [Adjust IP Adresses device in device to use single IP adresses](https://github.com/camaraproject/DeviceLocation/issues/117) + - Already done, to be closed when merged + - **Closed** with PR merging. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress + +* [security and scopes for the Device Location API](https://github.com/camaraproject/DeviceLocation/issues/105) + - Ludovic answered. + - **Closed** + +* [Documentation Updated](https://github.com/camaraproject/DeviceLocation/issues/102) + - part of https://github.com/camaraproject/DeviceLocation/pull/104 + - **Closed** with PR merging. + +### Open discussions + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - TEF provided a doc with a proposal and use cases for the implementation of 'Partial' and matchRate + - During previous meeting we agreed to use the formula defined in the Word document. + - Descriptions regarding partials and matchRate has been added in location-verification yaml + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + + +## AOB + +- Next call will be **January 16th, 2024** + +

                                                                    + diff --git a/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16.md b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16.md new file mode 100644 index 0000000000000000000000000000000000000000..aca10e9db3f83805a087f7f4b895b4111893f157 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-16.md @@ -0,0 +1,126 @@ +# CAMARA DeviceLocation meeting - 2024-01-16 + +*January 16th, 2024* + +## Attendees + +José Luis Urien Pinedo (Telefonica) +Joachim Dahlgren (Ericsson) +Akos Hunyadi (DT) +Cetin Alpaycetin (Vodafone) +Javier Carro Calador (Telefonica) +Ludovic Robert (Orange) +Nicholas Venezia (Centillion) +Jorge Garcia Hospital (Telefonica) +Foo Ming Hui (Singtel) +Fernando Prado Cabrillo (Tlefonica) + + + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2-rc2 + +- Release Candidate was created in [branch](https://github.com/camaraproject/DeviceLocation/tree/release-0.2.0-rc) +- Error detected after releasing, with enum values for Area, [already fixed](https://github.com/camaraproject/DeviceLocation/issues/131) +- [Prepare RC2](https://github.com/camaraproject/DeviceLocation/pull/134) PR already merged +- New errors reported, to be fixed in RC2: + - [Correct YAML examples to use upper case enum of areaType](https://github.com/camaraproject/DeviceLocation/issues/136) + - Create PR with fix + + - [Fix format for attribute lastLocationTime in location retrieval](https://github.com/camaraproject/DeviceLocation/issues/137) + - Create PR with fix + + - [Rename in the OAS SubscriptionEventType to NotificationEventType](https://github.com/camaraproject/DeviceLocation/issues/139) + - Create PR to change schema names + +- Create RC2 branch and release tag + - Ludovic will do for both API + - No change for the version in the yaml + +### Review other Issues and PRs + +#### New + + - [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - Review comments + - José answers in the PR + - Joachim agreed on the fact that make sense to have one event type both for left & entered + - Akos: The UC is clear - how we solve it + - One approach is to allow to subscribe to an array of event type + - Discussed in the past but adding an array of notification type will add a layer of complexity to manage a subscription + - Could be a problem if the server is not able to manago one kind of event type. + - **Keep it open to let the discussion open.** + - José will also check with development team + - Having both 'event' in one notification type could have an impact on the server managing the event + + - [Revise Description to Meet GDPR Compliance - REMOVAL OF " Location-based advertising" in Documentation](https://github.com/camaraproject/DeviceLocation/issues/135) + - Review comments + - Nicholas will propose a better wording for this sentence + - Could be integrated in rc2 + + - [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - Review comments + - Need more review from the team + - Correlation with issue [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - **keep the discussion open** + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status + - Proposal to use this one as the 'model sample' for Commonalities + - **Keep in open but need to be prioritized** + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Next steps + - Integrate the linting in our CI as for QoD + - As codeowner we did not have the right to add it. + - José will comment and ping Markus & Rafal to ask them how we can move forward. + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Review comments, next steps + - Probably same thing must be done for area left. + - Akos & Ludovic have UC where it could be necessary. + - Nicholas mentionned also ad-based UC (ad in a podcast location-based for example) where we want to control the time when the ad should be triggered for a device + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open in Commonalities + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - no progress in Commonalities + + +### Open discussions + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Next call will be **January 30th, 2024** + +

                                                                    + diff --git a/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30.md b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30.md new file mode 100644 index 0000000000000000000000000000000000000000..f573a8d45feef9c0c9c3f54b432be6cd9942d418 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-01-30.md @@ -0,0 +1,100 @@ +# CAMARA DeviceLocation meeting - 2024-01-30 + +*January 30th, 2024* + +## Attendees + +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* José Luis Urien Pinedo (Telefonica) +* Rafal Artych (DT) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2-rc2 + +- [PR](https://github.com/camaraproject/DeviceLocation/pull/142) with fixes to: + - [Correct YAML examples to use upper case enum of areaType](https://github.com/camaraproject/DeviceLocation/issues/136) + - [Fix format for attribute lastLocationTime in location retrieval](https://github.com/camaraproject/DeviceLocation/issues/137) + - [Rename in the OAS SubscriptionEventType to NotificationEventType](https://github.com/camaraproject/DeviceLocation/issues/139) + - [Revise Description to Meet GDPR Compliance - REMOVAL OF " Location-based advertising" in Documentation](https://github.com/camaraproject/DeviceLocation/issues/135) + +- AP: Give one more day for review, merge and create RC2 + +### Review other Issues and PRs + +#### New + + - [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Review comments. Cetin agrees with Ludovic's comment. + - AP: We'lll wait for Commonalities to add it to Geofencing. + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - Review new comments + - AP: Get more opinions. + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - Review new comments. + - AP: Get more opinions. + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - still open - Review new comments + - AP: Wait for outcome in Commonalities + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - José asked Markus & Rafal how we can move forward. + - Rafal explains that process will be: + - Merge PR in commonalities with the initial ruleset as an artifact. + - Possibly a discussion in TSC about how to add it in each WG in a common way. + - AP: We'll wait for the process. In the meantime we are able to test it locally and provide feedback before integrating. + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - No new comments + - AP: We are at a point where we can create a PR. Jose will ping Akos in case he wants to create the PR, otherwise Jose will create it to move the discussion to the PR. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - still open in Commonalities. No new comments. + - AP: Ping in the issue to reactivate the discussion + +### Open discussions + +- No new comments since last meeting. We keep these discussions on hold. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Next call will be **February 13th, 2024** + +

                                                                    + diff --git a/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13.md b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13.md new file mode 100644 index 0000000000000000000000000000000000000000..8f4b3bbab515da49493e4ad5c8625fd5784db4e1 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-13.md @@ -0,0 +1,143 @@ +# CAMARA DeviceLocation meeting - 2024-02-13 + +*February 13th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (DT) +* Javier Caaro Calabor (Telefonica) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Review v0.2.0-rc3 + +- [PR](https://github.com/camaraproject/DeviceLocation/pull/150) with fixes to: + - [fix: correct $ref for SubscriptionEventType in geofencing](https://github.com/camaraproject/DeviceLocation/pull/149) + - Some other fixes and enhancements detected by linter (locally) + +- Give some time review, merge and create RC3 +- If nothing else is detected, then create release-0.2.0 + +Discussed during meeting: +Action: Team has to review the PR. We have to work offline to release the API before the MWC. +Minor typo fixes (on subscription) +Feedback on Linting tool run + + +### Review other Issues and PRs + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. -> Still pending + +Discussed during meeting: +- José explained that first we need to provide variable(s) + - First then 'given' to prepare this/these variable(s) + - Then the result with the expected responses + - +Additionnal step oculd be used (ad hoc for specific operation) +- GSMA will test this files as an input for Conformance & using Postman. +- José will contribut to commonalities for guidelines for Test Definition + - Ludovic agreed on José proposal and will adapt the Device location retrieval file once José made his proposal. + + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Positive feedback + - How to proceed? Create PR and share with Commonalities or the open issue in Commonalities? + +Discussed during meeting: +- Ludovic will create an Issue in Commonalities. + + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - No new comments + - Discuss next steps in meeting + +Discussed during meeting: +- we went through the proposal on the issue as 4 options are described +- We keep it open for discussion +- Alignement with device status was discussed. + + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - Discuss next steps in meeting + + Discussed during meeting: + - no progress - need team review + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - New [PR](https://github.com/camaraproject/Commonalities/pull/131) + - Review status + +Discussed during meeting: +- in final step in commonalities - soon to be applied + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Tested locally before creating RC3 + - Review status in Commonalities + +Discussed during meeting: +- Rafal provided a briefting of the situation + - Still in discussion in commonalities + - Question to TSC if each projet has to be independant for applying the lintening. + - else José will apply the CI in our project + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments + +Discussed during meeting: +- No comments + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - Recent comment to reactivate the discussion + +Discussed during meeting: +- Team has to provide comment +- Rafal mentionned another issue about duration + + +### Open discussions + +- No new comments since last meeting. + + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - New [document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal +* [action] Review this document. + - Not progress but during last call we agreed that this feature is not top priority right now but will be discussed next year. + - Probably to keep it close with the (future) work for User Device count + - We can probably add our Area schemas in Commonalities + +This item should be reopen after MWC. + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + +- Discuss if we keep next call for February 27th, 2024, as it is the MWC week. + - We keep it + +

                                                                    diff --git a/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27.md b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27.md new file mode 100644 index 0000000000000000000000000000000000000000..b7ac4b0fcafa25c20c90c34452c5c071a948174e --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-02-27.md @@ -0,0 +1,115 @@ +# CAMARA DeviceLocation meeting - 2024-02-27 + +*February 27th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Akos Hunyadi (DT) +* Cetin Alpaycetin (Vodafone) +* Rafal Artych (DT) +* Javier Caaro Calabor (Telefonica) +* Foo Ming Hu (Singtel) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### Release 0.2.0 + + +- No new comments or bugs reported for [RC3](https://github.com/camaraproject/DeviceLocation/issues/155) + +- Discuss release approval + - **Agreed to release 0.2.0** + - AP @Jose: Create PR and make adjustments in Github. Remove RCs from Changelog if possible. + +### Review other Issues and PRs + +No new comments or progress on the ongoing issues and PRs + +#### Ongoing + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - Link with Commonalities here: https://github.com/camaraproject/Commonalities/issues/94 + - Review PR status and new comments + - AP: Telefónica will provide a proposal updating a few aspects of Ludovic's proposal after checking with internal QA team. + - Update by Jose, but still pending + + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + + AP from previous meeting: + - Ludovic will create an Issue in Commonalities. -> Pending, double check with Ludovic + - Related issues in [DeviceStatus](https://github.com/camaraproject/DeviceStatus/issues/117) and QoD + + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + + Discussed during previous meeting: + - Alignement with device status was discussed. + + - No specific issue created so far in Commonalities, but mentioned in [issue](https://github.com/camaraproject/Commonalities/issues/140) about CloudEvents Subscription format. + - This is not an urgent issue as functionality can be covered with current events, so we may wait until discussions in Commonalities advance. + + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - Connected with [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85). A document with implementation guideline should cover this also. + + +* [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/90) + - New [PR](https://github.com/camaraproject/Commonalities/pull/131) -> Still nor merged but seems to have all LGTM. AP: Double check with Ludovic + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - Tested locally before creating RC3 + - Review status in [Commonalities](https://github.com/camaraproject/Commonalities/issues/142) + - AP @Rafal to propose a PR adding linting to our subproject CI + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments in the issue in the last 2 weeks + - Discussed during the meeting if we should wait for Commonalities for a common format, or add parameters in our current model nad adapt later to approved guidelines. + - As we are starting cycle for a new release, we can wait for the moment. Eventually, if we are about to release something new and commonalities are not agreed, we can tale the lead. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - No comments in the last 2 weeks + - Wait for outcome + +### Open discussions + +- No new comments since last meeting. + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - [Document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal. + + This item should be reopen after MWC. + + - We should discussed approach on this for next release. Should we incorporate this to current operations, should we split this functionality to new endpoints or even separate APIs? + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + +## AOB + + - Joachim asked for plans or roadmap for R1.0 + - Jose commented that there is still no roadmap or time frame agreed for v1.0, but release plan for R1.0 should be agreed at CAMARA project level. + - At WG level we may discuss the content for next release, being 0.x or 1.x. So far we only have the requirement for Administrative Codes, but others may come from GSMA product track + +

                                                                    + +- Next call will be on **March 12th, 2024** + +

                                                                    + diff --git a/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12.md b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12.md new file mode 100644 index 0000000000000000000000000000000000000000..fa1f2cc7f7238f685751fa0ca42bb98969ccee56 --- /dev/null +++ b/original/DeviceLocation/documentation/MeetingMinutes/MoM-2024-03-12.md @@ -0,0 +1,138 @@ +# CAMARA DeviceLocation meeting - 2024-03-12 + +*March 12th, 2024* + +## Attendees + +* José Luis Urien (Telefonica) +* Joachim Dahlgren (Ericsson) +* Cetin Alpaycetin (Vodafone) +* Akos Hunyadi (DT) +* Javier Carro Calabor (Telefonica) +* Katrina Griese (Vodafone) +* Ludovic Robert (Orange) +* Alexander Boraczynski (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Rafal Artych (DT) +* Surajj Jaggernath (Vodacom) +* Toyeeb Rehman (GSMA) + +Device Location minutes: [https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceLocation/tree/main/documentation/MeetingMinutes) + + +> [!IMPORTANT] +> [Release 0.2.0](https://github.com/camaraproject/DeviceLocation/releases/tag/v0.2.0) official!! +> +> New merges to be consolidated towards next -wip versions + + +## Agenda + +* Open issues and PRs +* Any other business + +## Open issues and PRs + +### New + +#### Corrections + +* [[location-verification] Precise the description when matchRate needs to be set for PARTIAL-results](https://github.com/camaraproject/DeviceLocation/issues/158) + - Fixed in [PR 159](https://github.com/camaraproject/DeviceLocation/pull/159) + - Merged during the meeting. + +* [Add x-correlator as specified in the guideline](https://github.com/camaraproject/DeviceLocation/issues/160) + - PR to be created + - [Action] Ludovic will do + +* [subscriptionExpireTime is declared as "required" in the subscription-ends - note, but is optional currently](https://github.com/camaraproject/DeviceLocation/issues/161) +* Fixed along with old issue [Geofencing API - Adding capability to manage max number of notification](https://github.com/camaraproject/DeviceLocation/issues/111) + - Fixed in [PR 163](https://github.com/camaraproject/DeviceLocation/pull/163) + - Merged during the meeting + +* [[Geofencing]: Invalid area example for POST /subscriptions](https://github.com/camaraproject/DeviceLocation/issues/164) + - Fixed in [PR 165](https://github.com/camaraproject/DeviceLocation/pull/165) + -Merged during the meeting + +* [Remove API from info.title](https://github.com/camaraproject/DeviceLocation/issues/169) + - Remove API from the title + - [Action] José will create the PR + - Could be part of the linter rule but not yet + - action to standardize the info object + +#### Documentation + +* [Should 501 NOT_IMPLEMENTED be returned for unimplemented DeviceLocation APIs?](https://github.com/camaraproject/DeviceLocation/issues/168) + - Question related to the conformance + - Team agreed with José & Cetin comments + - Toyeeb aggreed + - Issue closed + + +#### Ongoing + +* [Implement use of linting rule set for Device Location API](https://github.com/camaraproject/DeviceLocation/issues/125) + - New PRs: [Introducing corrections for yamllint](https://github.com/camaraproject/DeviceLocation/pull/166) and [Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceLocation/pull/167) + - PR#166 Rafal will regenerate the linter & once done the PR will be merge + - PR#167: to be merged after #166 + - Can be done offline + +* [Add Test Definition for location Retrieval #119](https://github.com/camaraproject/DeviceLocation/pull/119/files) + - New issue in Commonalities to discuss [Enhancement of the Testing Guidelines](https://github.com/camaraproject/Commonalities/issues/158) by TEF + - [Action] José propose to make an example to illustrate his proposal + - [Action] Toyeeb to check with GSMA conformance + +* [Geofencing - Adding a value in Termination Reason value enum](https://github.com/camaraproject/DeviceLocation/issues/141) + - Ludovic will create an Issue in Commonalities. -> Pending, double check with Ludovic + - [Action] Yes Ludovic will create the PR in Commponalities + - Related issues in [DeviceStatus](https://github.com/camaraproject/DeviceStatus/issues/117) and QoD + +* [Geofencing API - Add Subscription type 'area-left-or-entered' to subscribe to both event in one time](https://github.com/camaraproject/DeviceLocation/issues/138) + - New issue in Commonalities [Subscription-Issue2: Allow event consumers to subscribe to more than one event types with a single subscription](https://github.com/camaraproject/Commonalities/issues/154) + - Waiting for Commonalities outcomes + +* [Geofencing API - Defining a standard behavior for first event](https://github.com/camaraproject/DeviceLocation/issues/124) + - Moved to Commonalities [Issue 140](https://github.com/camaraproject/Commonalities/issues/140) + - No comments in the issue in the last 2 weeks + - Waiting for Commonalities outcomes + +* [Define guidelines for geofencing implementation](https://github.com/camaraproject/DeviceLocation/issues/133) + - No new comments. + - [Action] We need more comments from the team + - Connected with [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85). A document with implementation guideline should cover this also. + +* [Geofencing API - Add "format: uri" to notificationUrl](https://github.com/camaraproject/DeviceLocation/issues/118) + - Moved to [commonalities](https://github.com/camaraproject/Commonalities/issues/93) + - No comments in the last 2 weeks + - Wait for outcome + +### Long term discussions + +#### Administrative Code Area + +* New [Issue #83](https://github.com/camaraproject/DeviceLocation/issues/83), with formal requirements from GSMA Product track + - [Document uploaded by TEF](https://github.com/camaraproject/DeviceLocation/files/12856149/AdminCode.Proposal.-.Draft_20230926.docx) with a proposal. + + This item should be reopen after MWC. + + - We should discussed approach on this for next release. Should we incorporate this to current operations, should we split this functionality to new endpoints or even separate APIs? + - Need to be discussed + - Ludovic preference is for a separate API as for example in France this is not a request. + - For Javier this is not a top priority for Telefonica as of now. + - More generally probably we need to have feedback loop with GSMA team about API work (and review the priority as focus could change) + - Perhaps a point to be share in TSC. + +#### Behaviour when requesting too high precision + +* [Issue #85](https://github.com/camaraproject/DeviceLocation/issues/85) + - As requested by Joachim, issue will remain open until TEF uploads the document with more detail or the information is added to an API_documentation file to keep in the repo for future references. + - Joachim: Should be also aligned/synchronysed with Geofencing + +## AOB + +

                                                                    + +- Next call will be on **March 26th, 2024** +- Easter week, but we keep the meeting + +

                                                                    diff --git a/original/DeviceLocation/documentation/SupportingDocuments/README.MD b/original/DeviceLocation/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceLocation/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceMediaStreamingRate/README.md b/original/DeviceMediaStreamingRate/README.md new file mode 100644 index 0000000000000000000000000000000000000000..5b0d5d79348db258cbd4d11a4b1d354d3c8c28ec --- /dev/null +++ b/original/DeviceMediaStreamingRate/README.md @@ -0,0 +1,41 @@ + + + + + + + + + +# DeviceMediaStreamingRate + +Sandbox API Repository to describe, develop, document, and test the DeviceMediaStreamingRate API within the Sub Project [DeviceStatus](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/GQCbBQ) + +## Scope + +* Service API “DeviceMediaStreamingRate” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the customer with the ability to: + * Get insights about the network status of a defined mobile device. + * For this the API will return an indicator which is bundeling information about the device network status such as availibilty, open datavolume, congjestion, historical congjestion or the connecitvity status (2G, 3G, 4G, 5G). + * This API would be useful for applications that optimize user experience based on the connecitvity status of a defined device. +* Describe, develop, document, and test the APIs +* Started: August 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings or Sub Project Device Status are held virtually + * Schedule: Bi-weekly on Wednesday, 11:00 CET/CEST (08:00 UTC, 09:00 UTC during European DST) + * [Registration / Join]([https://wiki.camaraproject.org/x/TQAG](https://zoom-lfx.platform.linuxfoundation.org/meeting/94783050047?password=c43ff9fd-4c79-468a-9d98-45222dd6343d)) + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/DeviceStatus+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceMediaStreamingRate/code/API_definitions/README.MD b/original/DeviceMediaStreamingRate/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/DeviceMediaStreamingRate/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate.yaml b/original/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate.yaml new file mode 100644 index 0000000000000000000000000000000000000000..64cbc7705492772e7492d4f32dc6e1ea2d31b8dd --- /dev/null +++ b/original/DeviceMediaStreamingRate/code/API_definitions/media-streaming-rate.yaml @@ -0,0 +1,575 @@ +openapi: 3.0.3 +info: + title: Media Streaming Rate + version: wip + x-camara-commonalities: 0.6 + description: | + This is a media streaming rate service API that allows application developers to retrieve + the maximum media streaming bit rate supported for a given device. + + # Introduction + The Media Streaming Rate API allows an application developer to query the network + for the maximum supported media streaming bit rate for a specific end user device. + This API measures device connection quality by determining the maximum downstream + data rate available for media streaming, which is influenced by factors such as + network conditions, device capabilities, and current network congestion. + + This information helps developers ensure their media streaming applications can provide + optimal quality while using the current network connection, enabling adaptive bitrate + streaming and preventing buffering issues. + + # API functionality + + Prerequisite: authorisation and authentication + + Usage: + 1. Request: POST `retrieve-maximum-downstream-media-rate`, passing device identification + information such as IP address, phone number, or network access identifier. + 2. Response: The network will return the maximum downstream media streaming bit rate supported + for the device along with the unit of measurement. + + # Usage in Media Streaming Applications + + This API can be integrated into media streaming applications to determine optimal + video resolution for streaming. A typical workflow: + + 1. Application client requests manifest file (DASH/HLS) from CDN server + 2. Application client calls Media Streaming Rate API to get maximum supported bit rate + 3. Based on the response, application selects appropriate media resolution from the manifest + 4. Application begins media streaming from CDN using the optimal resolution + + This approach ensures the best possible viewing experience while preventing buffering or quality issues. + + The diagram below illustrates how the Media Streaming Rate API is used in a typical media streaming application: + + ![Media Streaming Rate API Sequence Diagram](../../documentation/SupportingDocuments/media-rate-sequence-flow.png) + + # Token usage: two-legged vs three-legged + + This API supports two types of access tokens: + + - **Two-legged token**: Used for server-to-server calls. The device to be queried MUST be identified by providing the `device` object in the request body. + - **Three-legged token**: Used for user-authenticated calls. The device is identified from the access token itself, and the `device` object MUST NOT be provided in the request. + + If a two-legged token is used and the device object is missing, the API will return a `422 MISSING_IDENTIFIER` error. + If a three-legged token is used and the device object is provided, the API will return a `422 UNNECESSARY_IDENTIFIER` error. + + This approach ensures clarity and security in device identification, and aligns with CAMARA API standards. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the device object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation + url: https://github.com/camaraproject/DeviceQualityIndicator + +servers: + - url: "{apiRoot}/media-streaming-rate/vwip" + variables: + apiRoot: + default: http://localhost:8087 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Media Streaming Rate + description: | + Retrieve the maximum media streaming bit rate supported for a given device. + +paths: + /retrieve-maximum-downstream-media-rate: + post: + security: + - openId: + - media-streaming-rate:retrieve-maximum-downstream-media-rate + tags: + - Media Streaming Rate + summary: Get maximum downstream media streaming rate + description: | + Retrieve the maximum downstream media streaming rate for a device. This helps application + developers determine the optimal media quality settings for their applications. + + When using a two-legged token, the device object MUST be provided. + When using a three-legged token, the device object MUST NOT be provided as + the device information will be extracted from the token. + operationId: retrieveMaximumDownstreamMediaRate + parameters: + - name: x-correlator + in: header + required: false + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + description: Device information needed to determine media rate capabilities. + content: + application/json: + schema: + $ref: "#/components/schemas/Device" + required: true + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/MediaStreamingRateResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + +components: + securitySchemes: + openId: + type: openIdConnect + description: | + Common security scheme for all CAMARA APIs. + + Two types of tokens can be used with this API: + + 1. Two-legged token: Used for server-to-server calls where the device + information MUST be included in the request body. + + 2. Three-legged token: Used for user-authenticated calls where the device + information is extracted from the token itself. In this case, the + device object MUST NOT be included in the request. + + The specific authorization flows to be used will be agreed upon during + the onboarding process between the API consumer and the API provider. + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The + API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the same + device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + MediaStreamingRateResponse: + type: object + description: The maximum downstream media streaming bit rate supported for the device. + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + maxDownstreamMediaBitRateSupported: + type: integer + description: The maximum downstream bit rate supported for the device + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + type: string + description: The unit of the bit rate (e.g., Mbps, Kbps) + example: "Mbps" + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + required: + - maxDownstreamMediaBitRateSupported + - unit + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. diff --git a/original/DeviceMediaStreamingRate/documentation/API_documentation/README.MD b/original/DeviceMediaStreamingRate/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceMediaStreamingRate/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceMediaStreamingRate/documentation/SupportingDocuments/README.MD b/original/DeviceMediaStreamingRate/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceMediaStreamingRate/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceReachabilityStatus/README.md b/original/DeviceReachabilityStatus/README.md new file mode 100644 index 0000000000000000000000000000000000000000..7510ce6dee6253b047d38fffba55d1fb29e584d0 --- /dev/null +++ b/original/DeviceReachabilityStatus/README.md @@ -0,0 +1,61 @@ + + + + + + + + + +# DeviceReachabilityStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceReachabilityStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mwD1Bg) + +## Scope + +* Service API(s) “DeviceReachabilityStatus” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if a device is reachable or is not connected to the network + * receive notifications if the connectivity status of the device changes +* Describe, develop, document, and test the API(s) +* Started: July 2022 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) +* Incubating stage since: February 2025 (via DeviceStatus) + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DeviceReachabilityStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **device-reachability-status-subscriptions v0.8.0** + [[YAML]](https://github.com/camaraproject/DeviceReachabilityStatus/blob/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + * **device-reachability-status v1.1.0** + [[YAML]](https://github.com/camaraproject/DeviceReachabilityStatus/blob/r1.2/code/API_definitions/device-reachability-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceReachabilityStatus/r1.2/code/API_definitions/device-reachability-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceReachabilityStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceReachabilityStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceReachabilityStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions.yaml b/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..58e6e12d0c3dcbeec4cac31773e117a8fded6b42 --- /dev/null +++ b/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status-subscriptions.yaml @@ -0,0 +1,1774 @@ +openapi: 3.0.3 +info: + title: Device Reachability Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Reachability status events. + + # Introduction + + ## Reachability Status + API consumer is able to be notified whether the reachability status of a certain user device has changed to either data- or sms-usage. + This capability is provided via a subscription request - in this case the reachability situation is part of the event notification, which is sent back to the event subscriber when reachability situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes following capability: + + ## Device reachability status subscription + + These endpoints allow to manage event subscription on reachability device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data``: Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms``: Event triggered when the device is connected to the network only for SMS usage + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected``: Event triggered when the device is not connected. + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** reachability state of the device: + + | subscribed event-type | device reachability status at subscription time | event sent if ``initialEvent`` set to true | Explanation | + | ----------------------| ------------- | --------------- | ---------------| + | reachability-data | Device can use data | Yes | The device is reachable for data, so the event is triggered. | + | reachability-data | Device is disconnected or SMS-only | No | The device cannot use data, so no event is sent. | + | reachability-sms | Device can use data | No | The device can use data, but for thids event is only for SMS. | + | reachability-sms | Device is SMS-only | Yes | The device supports SMS, so the event is triggered. | + | reachability-sms | Device is disconnected | No | The device cannot send SMS, so no event is send. | + | reachability-disconnected | Device can use data or SMS usage | No | The device is reachable, so no "disconnected" event is sent. | + | reachability-disconnected | Device is disconnected | Yes | The device is disconnected, so the event is triggered. | + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which reachability status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide reachability status update notifications for the multi-SIM group as a whole, or + - provide reachability status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceReachabilityStatus + +servers: + - url: "{apiRoot}/device-reachability-status-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Device reachability status subscription + description: Operation to manage event subscription on device reachability status event. + +paths: + /subscriptions: + post: + tags: + - Device reachability status subscription + summary: "Create a device reachability status event subscription for a device" + description: Create a device reachability status event subscription for a device + operationId: createDeviceReachabilityStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device reachability status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + reachability-data: + $ref: "#/components/examples/REACHABILITY_DATA" + reachability-sms: + $ref: "#/components/examples/REACHABILITY_SMS" + reachability-disconnected: + $ref: "#/components/examples/REACHABILITY_DISCONNECTED" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device reachability status subscription + summary: "Retrieve a list of device reachability status event subscription" + description: Retrieve a list of device reachability status event subscription(s) + operationId: retrieveDeviceReachabilityStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-reachability-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device reachability status subscription + summary: "Retrieve a device reachability status event subscription for a device" + operationId: retrieveDeviceReachabilityStatusSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device reachability status subscription + summary: "Delete a device reachability status event subscription for a device" + operationId: deleteDeviceReachabilityStatusSubscription + description: Delete a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer subscribes to reachability SMS. If consumer sets initialEvent to true and device is already reachable by SMS, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage. + + reachability-disconnected - Event triggered when the device is not connected. + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends. + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data: "#/components/schemas/EventReachabilityData" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms: "#/components/schemas/EventReachabilitySms" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected: "#/components/schemas/EventReachabilityDisconnected" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + If the time of the occurrence cannot be determined then this attribute MAY be set to some other time (such as the current time) by the CloudEvents producer, + however all producers for the same source MUST be consistent in this respect. In other words, + either they all use the actual time of the occurrence or they all use the same algorithm to determine the value used. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2018-04-05T17:31:00Z" + + EventReachabilityData: + description: event structure for reachability data usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilitySms: + description: event structure for reachability SMS usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilityDisconnected: + description: event structure for disconnection + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + ReachabilityDataSmsDisconnected: + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnded: + description: Event structure for sending subscription-ended event + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + SubscriptionEnded: + description: Event detail structure for org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + REACHABILITY_DATA: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_SMS: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_DISCONNECTED: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a device reachability status subscription ends. + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-22T05:40:23.682Z" + + SUBSCRIPTION_STARTED: + description: The cloud event when a device reachability status subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a device reachability status subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] diff --git a/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status.yaml b/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status.yaml new file mode 100644 index 0000000000000000000000000000000000000000..5edb46504c47446531202317fbc78a7d282b3953 --- /dev/null +++ b/original/DeviceReachabilityStatus/code/API_definitions/device-reachability-status.yaml @@ -0,0 +1,555 @@ +openapi: 3.0.3 +info: + title: Device Reachability Status + description: | + This API provides the API consumer with the ability to query device reachability status. + + # Introduction + + ## Reachability Status + + API consumer is able to verify whether a certain user device is reachable from the network via data- or sms-usage. + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Reachable:** Indicates, if the device is reachable from the network or not. + + * **Connectivity:** Indicates the connectivity types (DATA, SMS or both) through which the device is reachable from the network. + + * **LastStatusTime** : The time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ### Device Reachability situation + + The endpoint `POST /retrieve` allows to get current connectivity status information synchronously. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the reachability status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined reachability status for the multi-SIM group as a whole, or + - return the reachability status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceReachabilityStatus + +servers: + - url: "{apiRoot}/device-reachability-status/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Device reachability status + description: Operations to get the current reachability status of a device +paths: + /retrieve: + post: + tags: + - Device reachability status + summary: "Get the current reachability status information" + description: Get the current reachability status information + operationId: getReachabilityStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RequestReachabilityStatus" + required: true + responses: + "200": + description: Contains information about current reachability status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ReachabilityStatusResponse" + examples: + Reachable Using SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Reachable Using SMS With Device Disambguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Reachable Using Data: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA"] + Reachable Using Data and SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA", "SMS"] + Not Reachable Over The Mobile Network: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: false + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + LastStatusTime: + description: | + The last time that the device reachability status was confirmed to be correct by the API provider. The status should still be valid, but the API provider is unable to confirm this. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ReachabilityStatusResponse: + type: object + required: + - lastStatusTime + - reachable + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + reachable: + description: Indicates overall device reachability + type: boolean + connectivity: + type: array + items: + $ref: "#/components/schemas/ConnectivityType" + + ConnectivityType: + description: | + DATA: The device is connected to the network for Data usage (regardless of the SMS reachability) + + SMS: The device is connected to the network only for SMS usage + + type: string + enum: + - DATA + - SMS + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + RequestReachabilityStatus: + description: The request to retrieve the current reachability status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue diff --git a/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..0c661524b0a4a468d1bd417cd644912d4a530ff1 --- /dev/null +++ b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md @@ -0,0 +1,25 @@ +# API Readiness Checklist + +Checklist for device-reachability-status 1.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-reachability-status.yaml](/code/API_definitions/device-reachability-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [device-reachability-status-User-Story.md](/documentation/API_documentation/device-reachability-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | See [here](https://github.com/camaraproject/DeviceReachabilityStatus/issues/44) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | See (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/2wHWB) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story.md b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..6ad4c751c761baa12d65002a7aaf25c7decfe015 --- /dev/null +++ b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-User-Story.md @@ -0,0 +1,20 @@ +# Device Reachability Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the reachability status of a user's device, so that I can determine whether the device is reachable via SMS, data (mobile internet), or both, enabling better communication or service management decisions based on real-time device availability. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                                                                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                                                                    **Scope:** Order To Activate (OTA) - Get connectivity status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                                                                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the reachability status of a user's device | M | +| Ends when | The service provider returns the reachability status of the device with a timestamp when the status information was updated. In case of the device is reachable, additionally, the type of the connectivity (data, sms or both) is returned as well. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                    - Incorrect input data (e.g., malformed phone number).
                                                                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) diff --git a/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..74618a18cca106c1542cae2ff84457c8df521733 --- /dev/null +++ b/original/DeviceReachabilityStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for device-reachability-status-subscriptions 0.8.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-reachability-status-subscriptions.yaml](/code/API_definitions/device-reachability-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-reachability-status-subscriptions.feature](/code/Test_definitions/device-reachability-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/JAFmBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceReachabilityStatus/documentation/SupportingDocuments/README.MD b/original/DeviceReachabilityStatus/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceReachabilityStatus/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceRoamingStatus/README.md b/original/DeviceRoamingStatus/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8610b55f9112ee6d8d63035a73151098df3e5863 --- /dev/null +++ b/original/DeviceRoamingStatus/README.md @@ -0,0 +1,61 @@ + + + + + + + + + +# DeviceRoamingStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceRoamingStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/127729674/DeviceRoamingStatus) + +## Scope + +* Service API(s) “DeviceRoamingStatus” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if a device is roaming, and in which country + * receive notifications if the roaming status of the device changes +* Describe, develop, document, and test the API(s) +* Started: July 2022 (within [DeviceStatus](https://github.com/camaraproject/DeviceStatus) repository) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/DeviceRoamingStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **device-roaming-status-subscriptions v0.8.0** + [[YAML]](https://github.com/camaraproject/DeviceRoamingStatus/blob/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + * **device-roaming-status v1.1.0** + [[YAML]](https://github.com/camaraproject/DeviceRoamingStatus/blob/r1.2/code/API_definitions/device-roaming-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceRoamingStatus/r1.2/code/API_definitions/device-roaming-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceRoamingStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceRoamingStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceRoamingStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions.yaml b/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f9ea5e4a951efeacef52dc625da4d157cc1def71 --- /dev/null +++ b/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status-subscriptions.yaml @@ -0,0 +1,1858 @@ +openapi: 3.0.3 +info: + title: Device Roaming Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Roaming status events. + + # Introduction + + ## Roaming Status + API consumer is able to be notified whether the roaming status of a certain user device has changed. + This capability is provided via a subscription request - in this case the roaming situation is not in the response but event notification is sent back to the event subscriber when roaming situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + # API Functionality + + The API exposes following capability: + + ## Device roaming status subscription + + These endpoints allow to manage event subscription on roaming device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `type` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status`` - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on`` - Event triggered when the device switch from roaming OFF to roaming ON + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off``: Event triggered when the device switch from roaming ON to roaming OFF + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country``: Event triggered when the device in roaming change country code + + Note: Additionally, the following events could be sent, which do not require a dedicated subscription: + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started` is sent when the subscription starts. + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated` is sent when the subscription is updated. + - `org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended` is sent when the subscription ends. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** roaming state of the device: + + | subscribed event-type | device roaming status at subscription time | event sent if ``initialEvent`` set to true | + | ----------------------| ------------- | --------------- | + | roaming-status | Roaming On | Yes | + | roaming-status | Roaming Off | Yes | + | roaming-on | Roaming On | Yes | + | roaming-on | Roaming Off | No | + | roaming-off | Roaming On | No | + | roaming-off | Roaming Off | Yes | + | roaming-change-country | Roaming Off | No(*) | + | roaming-change-country | Roaming On | No(*) | + + (*) Use of ``initialEvent`` has no impact on roaming-change-country event-type. + + **Clarification on ``roaming-change-country`` event-type:** + + ``roaming-change-country`` event is sent only when the device stays in roaming situation and change country. + Suppose a device from Germany & all event types subscribed: + + - Device moves from Germany to France: + - triggered: roaming-status & roaming-on + - not triggered: roaming-change-country & roaming-off + - Device moves from France to Belgium: + - triggered: roaming-change-country + - not triggered: roaming-status, roaming-on & roaming-off + - Device moves from Belgium back to Germany + - triggered: roaming-status & roaming-off + - not triggered: roaming-on & roaming-change-country + + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which roaming status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide roaming status update notifications for the multi-SIM group as a whole, or + - provide roaming status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceRoamingStatus + +servers: + - url: "{apiRoot}/device-roaming-status-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device roaming status subscription + description: Operation to manage event subscription on device roaming status event. + +paths: + /subscriptions: + post: + tags: + - Device roaming status subscription + summary: "Create a device roaming status event subscription for a device" + description: Create a device roaming status event subscription for a device + operationId: createDeviceRoamingStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device roaming status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + roaming-status: + $ref: "#/components/examples/ROAMING_STATUS" + roaming-change-country: + $ref: "#/components/examples/ROAMING_CHANGE_COUNTRY" + roaming-on: + $ref: "#/components/examples/ROAMING_ON" + roaming-off: + $ref: "#/components/examples/ROAMING_OFF" + subscription-started: + $ref: "#/components/examples/SUBSCRIPTION_STARTED" + subscription-updated: + $ref: "#/components/examples/SUBSCRIPTION_UPDATED" + subscription-ended: + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device roaming status subscription + summary: "Retrieve a list of device roaming status event subscription" + description: Retrieve a list of device roaming status event subscription(s) + operationId: retrieveDeviceRoamingStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-roaming-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + List of Subscriptions: + $ref: "#/components/examples/SUBSCRIPTION_LIST" + Empty List of Subscriptions: + $ref: "#/components/examples/EMPTY_SUBSCRIPTION_LIST" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device roaming status subscription + summary: "Retrieve a roaming status event subscription for a device" + description: retrieve device roaming status subscription information for a given subscription. + operationId: retrieveDeviceRoamingStatusSubscription + security: + - openId: + - device-roaming-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Active Subscription: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION" + Active Subscription With Device Disambiguation: + $ref: "#/components/examples/ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION" + Subscription Activation Requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + Subscription Deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device roaming status subscription + summary: "Delete a device-roaming-status event subscription for a device" + operationId: deleteDeviceRoamingStatusSubscription + description: Delete a given device-roaming-status subscription by ID + security: + - openId: + - device-roaming-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: device-roaming-status subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the current Commonalities version (v0.5) only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-started - Event triggered when the subscription starts. + + subscription-updated - Event triggered when the subscription is updated. + + subscription-ended - Event triggered when the subscription ends + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended + + SubscriptionEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status: "#/components/schemas/EventRoamingStatus" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country: "#/components/schemas/EventRoamingChangeCountry" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off: "#/components/schemas/EventRoamingOff" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on: "#/components/schemas/EventRoamingOn" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventRoamingStatus: + description: event structure for roaming status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingStatus" + + EventRoamingOn: + description: event structure for roaming on change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingOff: + description: event structure for roaming off change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingChangeCountry: + description: event structure for roaming change country + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingChangeCountry" + + EventSubscriptionEnded: + description: Event structure for sending subscription-ended event + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + EventSubscriptionStarted: + description: Event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + description: Description about the start of the subscription. + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: Event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + description: Description about the subscription update. + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + RoamingStatus: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - roaming + properties: + roaming: + type: boolean + description: Roaming status. True, if it is roaming. + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + RoamingChangeCountry: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + - countryName + properties: + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + SubscriptionEnded: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + required: + - terminationReason + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ROAMING_STATUS: + value: + id: "123654" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + roaming: true + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-17T13:18:23.682Z" + + ROAMING_OFF: + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-18T13:18:23.682Z" + + ROAMING_ON: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + ROAMING_CHANGE_COUNTRY: + value: + id: "123657" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + countryCode: 214 + countryName: ["ES"] + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDED: + description: The cloud event when a device roaming status subscription ends. + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_STARTED: + description: The cloud event when a device roaming status subscription was started. + value: + id: "124003" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-started + specversion: "1.0" + datacontenttype: application/json + data: + initiationReason: SUBSCRIPTION_CREATED + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_UPDATED: + description: The cloud event when a device roaming status subscription was updated. + value: + id: "124773" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-updated + specversion: "1.0" + datacontenttype: application/json + data: + updateReason: SUBSCRIPTION_ACTIVE + subscriptionId: qs15-h556-rt89-1298 + device: + phoneNumber: "+123456789" + time: "2024-03-05T15:00:23.682Z" + + ACTIVE_SUBSCRIPTION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + ACTIVE_SUBSCRIPTION_WITH_DEVICE_DISAMBIGUATION: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "xxx", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } + + SUBSCRIPTION_LIST: + description: A list of API consumer subscriptions. If a 3-legged access token is used, the list is specific to the device associated with that token. + value: + - id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: {} + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + EMPTY_SUBSCRIPTION_LIST: + description: The API consumer either has no subscriptions or, if a 3-legged access token is used, has none for the device associated with that token. + value: [] diff --git a/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status.yaml b/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status.yaml new file mode 100644 index 0000000000000000000000000000000000000000..45f216a47d2cdd857671583ba36d58341c1a8ca8 --- /dev/null +++ b/original/DeviceRoamingStatus/code/API_definitions/device-roaming-status.yaml @@ -0,0 +1,592 @@ +openapi: 3.0.3 +info: + title: Device Roaming Status + description: | + This API provides the API consumer with the ability to query device roaming Status + + # Introduction + + ## Roaming Status + API consumer is able to verify whether a certain user device is in roaming situation (or not). + + The verification of the roaming situation depends on the network's ability. Additionally to the roaming status, when the device is in roaming situation, visited country information could be returned in the response. + + ## Possible Use-Cases + Roaming status verification could be useful in scenario such as (not exhaustive): + - For regulatory reasons, where a customer may need to be within a certain jurisdiction, or out with others, in order for transactions to be authorized + - For security / fraud reasons, to establish that a customer is located where they claim to be + - For service delivery reasons, to ensure that the customer has access to particular service, and will not incur roaming charges in accessing them + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + + At least one identifier for the device (user equipment) out of four options must be provided: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session creation response. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Roaming** : Roaming status - `true`, if device is in roaming situation - `false` else. + + * **Country** : Country code and name - visited country information, provided if the device is in roaming situation. + + * **LastStatusTime** : The time when the status was last confirmed to be correct. An older status is more likely to now be incorrect. + + # API Functionality + + The API exposes following capabilities: + + ## Device roaming situation + + The endpoint `POST /retrieve` allows to get roaming status and country information (if device in roaming situation) synchronously. + + # Further info and support + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the roaming status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined roaming status for the multi-SIM group as a whole, or + - return the roaming status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceRoamingStatus + +servers: + - url: "{apiRoot}/device-roaming-status/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Roaming status retrieval + description: Operation to get device roaming status and country information (if roaming) synchronously +paths: + /retrieve: + post: + tags: + - Roaming status retrieval + summary: "Get the current roaming status and the country information" + description: Get the current roaming status and the country information + operationId: getRoamingStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusRequest" + examples: + INPUT_PHONE_NUMBER: + summary: Phone number + description: Retrieve roaming status for a device identified by a phone number + value: + device: + phoneNumber: "+123456789" + INPUT_IP_ADDRESS_V4: + summary: IPv4 address + description: Retrieve roaming status for a device identified by an IPv4 address + value: + device: + ipv4Address: + publicAddress: "123.234.1.2" + publicPort: 1234 + INPUT_IP_ADDRESS_V6: + summary: IPv6 address + description: Retrieve roaming status for a device identified by an IPv6 address + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + INPUT_NO_DEVICE: + summary: Device not provided + description: The device has to be deducted from token + value: + {} + required: true + responses: + "200": + description: Contains information about current roaming status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusResponse" + examples: + Not Roaming: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: false + No Country Name: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 901 + countryName: [] + Single Country Code: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Single Country Code With Device Disambiguation: + value: + device: + phoneNumber: "+123456789" + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Multiple Country Names: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 340 + countryName: ["BL", "GF", "GP", "MF", "MQ"] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + RoamingStatusResponse: + type: object + required: + - lastStatusTime + - roaming + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + roaming: + $ref: "#/components/schemas/ActiveRoaming" + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + LastStatusTime: + description: | + The last time that the device roaming status was confirmed to be correct by the API provider. It might not be possible to provide the current status because, for example, the device may not be connected to any mobile network. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ActiveRoaming: + description: Roaming status. True, if it is roaming + type: boolean + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + RoamingStatusRequest: + description: The request for retrieving the current roaming status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue diff --git a/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..3e2f6f9d8684097bcd9774872e3b44cb6fe6b8f1 --- /dev/null +++ b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md @@ -0,0 +1,25 @@ +# API Readiness Checklist + +Checklist for device-roaming-status 1.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-roaming-status.yaml](/code/API_definitions/device-roaming-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [device-roaming-status-User-Story.md](/documentation/API_documentation/device-roaming-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | See [here](https://github.com/camaraproject/DeviceRoamingStatus/issues/46) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | See (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/vYBmBQ) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story.md b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..605559aad78f50e8c137d358cc325cc070fe8070 --- /dev/null +++ b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-User-Story.md @@ -0,0 +1,21 @@ +# Device Roaming Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the roaming status of a user's device, so that I can determine whether a device is in a foreign network and in which country it is located. This API can be used to identify fraud, ensure regulatory compliance, or enforce territorial restrictions on video and audio content. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                                                                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                                                                    **Scope:** Order To Activate (OTA) - Get roaming status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                                                                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the roaming status of a user's device | M | +| Ends when | The service provider returns the roaming status of the device with a timestamp when the status information was updated. In case of a roaming situation also the roaming country name and code shall be returned. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                    - Incorrect input data (e.g., malformed phone number).
                                                                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) + diff --git a/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..f873e015c7d56f2ac8841d19ff46c8203aa032bc --- /dev/null +++ b/original/DeviceRoamingStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for device-roaming-status-subscriptions 0.8.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [device-roaming-status-subscriptions.yaml](/code/API_definitions/device-roaming-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [device-roaming-status-subscriptions.feature](/code/Test_definitions/device-roaming-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/D4FlBQ) | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceRoamingStatus/documentation/SupportingDocuments/README.MD b/original/DeviceRoamingStatus/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceRoamingStatus/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceStatus/README.md b/original/DeviceStatus/README.md new file mode 100644 index 0000000000000000000000000000000000000000..d917934091f384b6d285bdb9ae5d84ea3a26ae9c --- /dev/null +++ b/original/DeviceStatus/README.md @@ -0,0 +1,82 @@ + + + + + + + + + +# DeviceStatus + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceStatus Service API(s) within the Sub Project [Device Status](https://lf-camaraproject.atlassian.net/wiki/x/6wApBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) + +> [!WARNING] +> After the Camara Spring25 meta release this repository has been separated into 3 individual repositories: +> - [Device Roaming Status](https://github.com/camaraproject/DeviceRoamingStatus) +> - [Device Reachability Status](https://github.com/camaraproject/DeviceReachabilityStatus) +> - [Connected Network Type](https://github.com/camaraproject/ConnectedNetworkType) +> +> This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + +## Scope +* Service APIs for “Device Status” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + - check if a device is reachable or is not connected to the network + - check if a device is roaming, and in which country + - receive notifications if the connectivity or roaming status of the device changes +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/DeviceStatus/releases/tag/r2.2) (Spring25), with the following API versions: + * **connected-network-type-subscriptions v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type-subscriptions.yaml) + * **connected-network-type v0.1.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/connected-network-type.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/connected-network-type.yaml) + * **device-reachability-status-subscriptions v0.7.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status-subscriptions.yaml) + * **device-reachability-status v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-reachability-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-reachability-status.yaml) + * **device-roaming-status-subscriptions v0.7.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status-subscriptions.yaml) + * **device-roaming-status v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceStatus/blob/r2.2/code/API_definitions/device-roaming-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceStatus/r2.2/code/API_definitions/device-roaming-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * Bi-weekly on Wednesday, 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/93413850406?password=3aeb0f1b-d9f9-42c5-91d8-3d2b20421ef1) + * Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fzLe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-dst. + * A message to the community of this Sub Project can be sent using . + diff --git a/original/DeviceStatus/code/API_definitions/connected-network-type-subscriptions.yaml b/original/DeviceStatus/code/API_definitions/connected-network-type-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fa6399e98a3344ce5b49b728ef570b8ef2f80121 --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/connected-network-type-subscriptions.yaml @@ -0,0 +1,1497 @@ +openapi: 3.0.3 +info: + title: Connected Network Type Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to notifications on changes to the connected network type of a device. + + # Introduction + + ## Connected Network Type Subscription + API consumers can subscribe to receive notifications when the connected network type of a device changes. These notifications are delivered through CloudEvents. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Connected Network Type**: This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`: if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`: if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`: if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`: if device is connected to the 5G network technology + - `UNKNOWN`: if connection [technology] can not be determined + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type Subscription Management + + These endpoints allow you to manage subscriptions for receiving notifications on changes to the connected network type of a device. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed``: This event is triggered when the connected network type of the device changes. + + Note: Additionally, the event `org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + When ``initialEvent`` is set to ``true`` in the subscription request, a notification has to be sent immediately to provide the connected network type of the device targeted. + Note: If the status can not be determined, or if the device is not connected, we send an inital event with ``connectedNetworkType`` valued to`UNKNOWN`. + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding connected network type can be received from the service provider. + If an event occurs the application will send events to the provided webhook - 'sink'._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which connected network type notifications should be generated. If the phone number is used as the device identifier when creating a subscription in a multi-SIM scenario, the API may: + - respond with an error, or + - generate network type change notifications for the multi-SIM group as a whole, or + - generate network type change notifications for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/connected-network-type-subscriptions/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Connected Network Type Subscription + description: Operations to manage subscriptions for receiving notifications on changes to the connected network type of a device. + +paths: + /subscriptions: + post: + tags: + - Connected Network Type Subscription + summary: "Create a subscription for receiving notifications on changes to the connected network type of a device" + description: Create a subscription for receiving notifications on changes to the connected network type of a device. + operationId: createConnectedNetworkTypeSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever the connected network type of the device changes. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + network-type-changed: + $ref: "#/components/examples/NETWORK_TYPE_CHANGED" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created (Successful creation of subscription) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a list of device connected network type event subscription" + description: Retrieve a list of device connected network type event subscription(s) + operationId: retrieveConnectedNetworkTypeSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - connected-network-type-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Connected Network Type Subscription + summary: "Retrieve a device connected network type event subscription for a device" + description: retrieve ConnectedNetworkType subscription information for a given subscription ID. + operationId: retrieveConnectedNetworkTypeSubscription + security: + - openId: + - connected-network-type-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + Subscription Details: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Connected Network Type Subscription + summary: "Delete connected network type event subscription for a device" + operationId: deleteConnectedNetworkTypeSubscription + description: delete a given ConnectedNetworkType subscription. + security: + - openId: + - connected-network-type-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: ConnectedNetworkType subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + description: The error info object for possible error cases + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer request area entered event. If consumer sets initialEvent to true and device is already in the geofence, an event is triggered + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ConnectedNetworkType: + type: string + description: Network Type is intended to provide insight to connected network's capabilities from standards perspective. Actual network capabilities may differ based on implementation and MUST be checked with the connected network provider. + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + - org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + network-type-changed - Event triggered when the connected network type of the device changes. + enum: + - org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed: "#/components/schemas/EventNetworkTypeChange" + org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventNetworkTypeChange: + description: event structure for network type change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/EventNetworkTypeChangeData" + + EventNetworkTypeChangeData: + description: Event detail structure for network type changed data events + type: object + required: + - connectedNetworkType + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + SubscriptionEnds: + description: Event detail structure for SUBSCRIPTION_ENDS event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + NETWORK_TYPE_CHANGED: + description: The cloud event when a connected network type changed + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + specversion: "1.0" + datacontenttype: application/json + data: + subscriptionId: "987654321" + device: + phoneNumber: "+123456789" + connectedNetworkType: 5G + time: "2023-03-22T05:40:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "124003" + source: https://dataUsageServer.supertelco.com + type: "org.camaraproject.connected-network-type-subscriptions.v0.subscription-ends" + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: dv10-h556-rt89-1403 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-05T15:00:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.connected-network-type-subscriptions.v0.network-type-changed" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } diff --git a/original/DeviceStatus/code/API_definitions/connected-network-type.yaml b/original/DeviceStatus/code/API_definitions/connected-network-type.yaml new file mode 100644 index 0000000000000000000000000000000000000000..68dc5bf6bacabf74eeb0cf52f50b4fb1e743adaa --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/connected-network-type.yaml @@ -0,0 +1,492 @@ +openapi: 3.0.3 +info: + title: Connected Network Type + description: | + This API provides the customer with the ability to query to which Mobile Communication Technology it is connected to. + + # Introduction + + ## Connected Network Type + + The API consumer is able to query the device's connected network type. The API provider can determine this in various ways. For example, the network type can be inferred from the specific radio cell to which the device is connected, as radio cells only support a single technology. It is important to note that the API does not query the device directly. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the mobile network operator for the device. + + * **Connected Network Type** : This Type identifies the mobile technology of the network that the device is connected to (e.g. 4G, 5G, etc). It is the same as what is displayed on the device (e.g. on mobile phones). When the device moves across different areas of the network, the technology may change. As each technology is different, network capabilities may differ and MUST be checked with the API provider. + - `2G`, if device is connected to the 2G network technology (alternative indicators such as "G" or "E" may be displayed on the device) + - `3G`, if device is connected to the 3G network technology (alternative indicators such as "H" or "H+" may be displayed on the device) + - `4G`, if device is connected to the 4G network technology (alternative indicators such as "LTE" or "LTE+" may be displayed on the device) + - `5G`, if device is connected to the 5G network technology + - `UNKNOWN` if connection [technology] can not be determined + + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ## Connected Network Type + + The endpoint `POST /retrieve` allows to get connected Network Type. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which the connected network type should be returned. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a common connected network type for the multi-SIM group as a whole, or + - return the connected network type for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/connected-network-type/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Connected Network Type + description: Operations to get the network type device is connected to +paths: + /retrieve: + post: + tags: + - Connected Network Type + summary: "Get the connected network type" + description: Get the connected network type to which the user device is connected + operationId: getConnectedNetworkType + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - connected-network-type:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeRequest" + required: true + responses: + "200": + description: Contains connected network type + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ConnectedNetworkTypeResponse" + examples: + Connected-to-4G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 4G + Connected-to-5G: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: 5G + Connected-to-Undetermined: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + connectedNetworkType: UNKNOWN + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + LastStatusTime: + description: Last time that the associated connected Network Type was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ConnectedNetworkTypeResponse: + type: object + required: + - connectedNetworkType + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + connectedNetworkType: + $ref: "#/components/schemas/ConnectedNetworkType" + + ConnectedNetworkType: + description: | + * UNKNOWN: Used when connection [technology] can not be determined + * 2G: 2nd Generation Mobile Communication Technology + * 3G: 3rd Generation Mobile Communication Technology + * 4G: 4th Generation Mobile Communication Technology + * 5G: 5th Generation Mobile Communication Technology + + type: string + enum: + - 2G + - 3G + - 4G + - 5G + - UNKNOWN + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ConnectedNetworkTypeRequest: + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions.yaml b/original/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e96920c59ff7d16988d1a033e7e19f3a0844f56f --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/device-reachability-status-subscriptions.yaml @@ -0,0 +1,1602 @@ +openapi: 3.0.3 +info: + title: Device Reachability Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Reachability status events. + + # Introduction + + ## Reachability Status + API consumer is able to be notified whether the reachability status of a certain user device has changed to either data- or sms-usage. + This capability is provided via a subscription request - in this case the reachability situation is part of the event notification, which is sent back to the event subscriber when reachability situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + # API Functionality + + The API exposes following capability: + + ## Device reachability status subscription + + These endpoints allow to manage event subscription on reachability device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `types` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``types`` are managed for this API: + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data``: Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms``: Event triggered when the device is connected to the network only for SMS usage + + - ``org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected``: Event triggered when the device is not connected. + + Note: Additionally to these list, ``org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** reachability state of the device: + + | subscribed event-type | device reachability status at subscription time | event sent if ``initialEvent`` set to true | Explanation | + | ----------------------| ------------- | --------------- | ---------------| + | reachability-data | Device can use data | Yes | The device is reachable for data, so the event is triggered. | + | reachability-data | Device is disconnected or SMS-only | No | The device cannot use data, so no event is sent. | + | reachability-sms | Device can use data | No | The device can use data, but for thids event is only for SMS. | + | reachability-sms | Device is SMS-only | Yes | The device supports SMS, so the event is triggered. | + | reachability-sms | Device is disconnected | No | The device cannot send SMS, so no event is send. | + | reachability-disconnected | Device can use data or SMS usage | No | The device is reachable, so no "disconnected" event is sent. | + | reachability-disconnected | Device is disconnected | Yes | The device is disconnected, so the event is triggered. | + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which reachability status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide reachability status update notifications for the multi-SIM group as a whole, or + - provide reachability status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-reachability-status-subscriptions/v0.7" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. api.example.com or api.example.com/somepath + +tags: + - name: Device reachability status subscription + description: Operation to manage event subscription on device reachability status event. + +paths: + /subscriptions: + post: + tags: + - Device reachability status subscription + summary: "Create a device reachability status event subscription for a device" + description: Create a device reachability status event subscription for a device + operationId: createDeviceReachabilityStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms:create + - device-reachability-status-subscriptions:org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device reachability status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + reachability-data: + $ref: "#/components/examples/REACHABILITY_DATA" + reachability-sms: + $ref: "#/components/examples/REACHABILITY_SMS" + reachability-disconnected: + $ref: "#/components/examples/REACHABILITY_DISCONNECTED" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device reachability status subscription + summary: "Retrieve a list of device reachability status event subscription" + description: Retrieve a list of device reachability status event subscription(s) + operationId: retrieveDeviceReachabilityStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-reachability-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device reachability status subscription + summary: "Retrieve a device reachability status event subscription for a device" + operationId: retrieveDeviceReachabilityStatusSubscription + description: Retrieve a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + subscription-activation-requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + subscription-deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device reachability status subscription + summary: "Delete a device reachability status event subscription for a device" + operationId: deleteDeviceReachabilityStatusSubscription + description: Delete a given subscription by ID + security: + - openId: + - device-reachability-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer subscribes to reachability SMS. If consumer sets initialEvent to true and device is already reachable by SMS, an event is triggered. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + - org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + reachability-data - Event triggered when the device is connected to the network for Data usage (regardless of the SMS reachability). + + reachability-sms - Event triggered when the device is connected to the network only for SMS usage + + reachability-disconnected - Event triggered when the device is not connected. + + enum: + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + - org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: For the current Commonalities API design guidelines, only one event type per subscription is allowed + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data: "#/components/schemas/EventReachabilityData" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms: "#/components/schemas/EventReachabilitySms" + org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected: "#/components/schemas/EventReachabilityDisconnected" + org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. + If the time of the occurrence cannot be determined then this attribute MAY be set to some other time (such as the current time) by the CloudEvents producer, + however all producers for the same source MUST be consistent in this respect. In other words, + either they all use the actual time of the occurrence or they all use the same algorithm to determine the value used. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2018-04-05T17:31:00Z" + + EventReachabilityData: + description: event structure for reachability data usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilitySms: + description: event structure for reachability SMS usage + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + EventReachabilityDisconnected: + description: event structure for disconnection + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ReachabilityDataSmsDisconnected" + + ReachabilityDataSmsDisconnected: + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + SubscriptionEnds: + description: Event detail structure for org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends event + type: object + required: + - terminationReason + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + REACHABILITY_DATA: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_SMS: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-sms + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + REACHABILITY_DISCONNECTED: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.reachability-disconnected + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-reachability-status-subscriptions.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + terminationDescription: Subscription expiry time has been reached + time: "2024-03-22T05:40:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-reachability-status-subscriptions.v0.reachability-data" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } diff --git a/original/DeviceStatus/code/API_definitions/device-reachability-status.yaml b/original/DeviceStatus/code/API_definitions/device-reachability-status.yaml new file mode 100644 index 0000000000000000000000000000000000000000..0e489210399072bf7402fda8a81cc954452f71a8 --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/device-reachability-status.yaml @@ -0,0 +1,531 @@ +openapi: 3.0.3 +info: + title: Device Reachability Status + description: | + This API provides the API consumer with the ability to query device reachability status. + + # Introduction + + ## Reachability Status + + API consumer is able to verify whether a certain user device is reachable from the network via data- or sms-usage. + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Reachable:** Indicates, if the device is reachable from the network or not. + + * **Connectivity:** Indicates the connectivity types (DATA, SMS or both) through which the device is reachable from the network. + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ### Device Reachability situation + + The endpoint `POST /retrieve` allows to get current connectivity status information synchronously. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the reachability status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined reachability status for the multi-SIM group as a whole, or + - return the reachability status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 1.0.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-reachability-status/v1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Device reachability status + description: Operations to get the current reachability status of a device +paths: + /retrieve: + post: + tags: + - Device reachability status + summary: "Get the current reachability status information" + description: Get the current reachability status information + operationId: getReachabilityStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-reachability-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RequestReachabilityStatus" + required: true + responses: + "200": + description: Contains information about current reachability status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ReachabilityStatusResponse" + examples: + Connected-With-SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["SMS"] + Connected-With-DATA: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA"] + + Connected-With-DATA-And-SMS: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: true + connectivity: ["DATA", "SMS"] + Not-Reachable: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + reachable: false + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + LastStatusTime: + description: Last time that the associated device reachability status was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + ReachabilityStatusResponse: + type: object + required: + - reachable + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + reachable: + description: Indicates overall device reachability + type: boolean + connectivity: + type: array + items: + $ref: "#/components/schemas/ConnectivityType" + ConnectivityType: + description: | + DATA: The device is connected to the network for Data usage (regardless of the SMS reachability) + + SMS: The device is connected to the network only for SMS usage + + type: string + enum: + - DATA + - SMS + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + RequestReachabilityStatus: + description: The request to retrieve the current roaming-status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue diff --git a/original/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions.yaml b/original/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..b4715705a1446c5980ee77152c0db3787cfbb531 --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/device-roaming-status-subscriptions.yaml @@ -0,0 +1,1709 @@ +openapi: 3.0.3 +info: + title: Device Roaming Status Subscriptions + description: | + This API provides the API consumer with the ability to subscribe to Roaming status events. + + # Introduction + + ## Roaming Status + API consumer is able to be notified whether the roaming status of a certain user device has changed. + This capability is provided via a subscription request - in this case the roaming situation is not in the response but event notification is sent back to the event subscriber when roaming situation has changed. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + # API Functionality + + The API exposes following capability: + + ## Device roaming status subscription + + These endpoints allow to manage event subscription on roaming device status event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + When subscribing, it is mandatory to provide the event `type` you are subscribing to, as multiple subscription-types are managed by this API. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status`` - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on`` - Event triggered when the device switch from roaming OFF to roaming ON + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off``: Event triggered when the device switch from roaming ON to roaming OFF + + - ``org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country``: Event triggered when the device in roaming change country code + + Note: Additionally to these list, ``org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used in following cases: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the Access Token `sinkCredential` (optionally set by the requester) expiration time has been reached + - the API server has to stop sending notification prematurely + + **Note on combined usage of ``initialEvent`` and ``subscriptionMaxEvents``**: + + If an event is triggered following ``initialEvent`` set to true, + this event will be counted towards ``subscriptionMaxEvents`` (if provided). + + **Clarification on ``initialEvent`` & ``event-type`` behaviour:** + + Following table illustrate behaviour regarding event triggering depending on **initial** roaming state of the device: + + | subscribed event-type | device roaming status at subscription time | event sent if ``initialEvent`` set to true | + | ----------------------| ------------- | --------------- | + | roaming-status | Roaming On | Yes | + | roaming-status | Roaming Off | Yes | + | roaming-on | Roaming On | Yes | + | roaming-on | Roaming Off | No | + | roaming-off | Roaming On | No | + | roaming-off | Roaming Off | Yes | + | roaming-change-country | Roaming Off | No(*) | + | roaming-change-country | Roaming On | No(*) | + + (*) Use of ``initialEvent`` has no impact on roaming-change-country event-type. + + **Clarification on ``roaming-change-country`` event-type:** + + ``roaming-change-country`` event is sent only when the device stays in roaming situation and change country. + Suppose a device from Germany & all event types subscribed: + + - Device moves from Germany to France: + - triggered: roaming-status & roaming-on + - not triggered: roaming-change-country & roaming-off + - Device moves from France to Belgium: + - triggered: roaming-change-country + - not triggered: roaming-status, roaming-on & roaming-off + - Device moves from Belgium back to Germany + - triggered: roaming-status & roaming-off + - not triggered: roaming-on & roaming-change-country + + + ### Notifications callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. + As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + _**WARNING**: This callback endpoint must be exposed on the consumer side as `POST /{$request.body#/sink}`. + Developers may provide a callback URL on which notifications regarding reachability-status can be received from the service provider. + If an event occurs the application will send events to the provided webhook - `sink`._ + + # Further info and support + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ### Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify from that phone number the device for which roaming status notifications should be provided. If the phone number is used as the device identifier when creating a subscription for a multi-SIM scenario, the API may: + - respond with an error, or + - provide roaming status update notifications for the multi-SIM group as a whole, or + - provide roaming status update notifications only for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-roaming-status-subscriptions/v0.7" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device roaming status subscription + description: Operation to manage event subscription on device roaming status event. + +paths: + /subscriptions: + post: + tags: + - Device roaming status subscription + summary: "Create a device roaming status event subscription for a device" + description: Create a device roaming status event subscription for a device + operationId: createDeviceRoamingStatusSubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off:create + - device-roaming-status-subscriptions:org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country:create + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + Create Subscription: + $ref: "#/components/examples/CREATE_SUBSCRIPTION" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The Device status server will call this endpoint whenever any device roaming status related event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + roaming-status: + $ref: "#/components/examples/ROAMING_STATUS" + roaming-change-country: + $ref: "#/components/examples/ROAMING_CHANGE_COUNTRY" + roaming-on: + $ref: "#/components/examples/ROAMING_ON" + roaming-off: + $ref: "#/components/examples/ROAMING_OFF" + subscription-ends: + $ref: "#/components/examples/SUBSCRIPTION_ENDS" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Device roaming status subscription + summary: "Retrieve a list of device roaming status event subscription" + description: Retrieve a list of device roaming status event subscription(s) + operationId: retrieveDeviceRoamingStatusSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - device-roaming-status-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + + /subscriptions/{subscriptionId}: + get: + tags: + - Device roaming status subscription + summary: "Retrieve a roaming status event subscription for a device" + description: retrieve device roaming status subscription information for a given subscription. + operationId: retrieveDeviceRoamingStatusSubscription + security: + - openId: + - device-roaming-status-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + subscription-active: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVE" + subscription-activation-requested: + $ref: "#/components/examples/SUBSCRIPTION_ACTIVATION_REQUESTED" + subscription-deleted: + $ref: "#/components/examples/SUBSCRIPTION_DELETED" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + + delete: + tags: + - Device roaming status subscription + summary: "Delete a device-roaming-status event subscription for a device" + operationId: deleteDeviceRoamingStatusSubscription + description: Delete a given device-roaming-status subscription by ID + security: + - openId: + - device-roaming-status-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: device-roaming-status subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the current Commonalities version (v0.5) only one event type per subscription is allowed, yet in the following releases use of array of event types SHALL be specified without changing this definition. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request.Up to API project decision to keep it. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + EventTypeNotification: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + + SubscriptionEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: url + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + example: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + NotificationEventType: + type: string + description: | + roaming-status - Event triggered when the device switch from roaming ON to roaming OFF and conversely + + roaming-on - Event triggered when the device switch from roaming OFF to roaming ON + + roaming-off - Event triggered when the device switch from roaming ON to roaming OFF + + roaming-change-country - Event triggered when the device in roaming change country code + + subscription-ends - Event triggered when the subscription is terminated + enum: + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + - org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + - org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + + SubscriptionAsync: + description: Response for a device reachability status operation managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/r2.3/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status: "#/components/schemas/EventRoamingStatus" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country: "#/components/schemas/EventRoamingChangeCountry" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off: "#/components/schemas/EventRoamingOff" + org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on: "#/components/schemas/EventRoamingOn" + org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends: "#/components/schemas/EventSubscriptionEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: "2018-04-05T17:31:00Z" + + EventRoamingStatus: + description: event structure for roaming status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingStatus" + + EventRoamingOn: + description: event structure for roaming on change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingOff: + description: event structure for roaming off change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/BasicDeviceEventData" + + EventRoamingChangeCountry: + description: event structure for roaming change country + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/RoamingChangeCountry" + + EventSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnds" + + BasicDeviceEventData: + description: Event detail structure for basic device events + type: object + required: + - subscriptionId + properties: + device: + $ref: "#/components/schemas/Device" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + RoamingStatus: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - roaming + properties: + roaming: + type: boolean + description: Roaming status. True, if it is roaming. + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + RoamingChangeCountry: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + - countryName + properties: + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + SubscriptionEnds: + description: Event detail structure for org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends event + allOf: + - $ref: "#/components/schemas/BasicDeviceEventData" + - type: object + required: + - countryCode + required: + - terminationReason + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ROAMING_STATUS: + value: + id: "123654" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + roaming: true + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-17T13:18:23.682Z" + + ROAMING_OFF: + value: + id: "123655" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-off + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-18T13:18:23.682Z" + + ROAMING_ON: + value: + id: "123656" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + ROAMING_CHANGE_COUNTRY: + value: + id: "123657" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.roaming-change-country + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + countryCode: 214 + countryName: ["ES"] + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: https://notificationSendServer12.supertelco.com + type: org.camaraproject.device-roaming-status-subscriptions.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + device: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: qs15-h556-rt89-1298 + time: "2023-01-19T13:18:23.682Z" + + SUBSCRIPTION_ACTIVE: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVE + + SUBSCRIPTION_ACTIVATION_REQUESTED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: ACTIVATION_REQUESTED + + SUBSCRIPTION_DELETED: + value: + id: 550e8400-e29b-41d4-a716-446655440000 + sink: https://endpoint.example.com/sink + protocol: HTTP + types: + - "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-on" + config: + subscriptionDetail: + device: + phoneNumber: "+123456789" + subscriptionExpireTime: "2024-07-17T13:18:23.682Z" + subscriptionMaxEvents: 5 + initialEvent: true + startsAt: "2024-07-03T21:12:02.871Z" + expiresAt: "2024-07-03T21:12:02.871Z" + status: DELETED + + CREATE_SUBSCRIPTION: + value: + sink: "https://endpoint.example.com/sink" + sinkCredential: { + "credentialType": "ACCESSTOKEN", + "accessToken": "JhbGciOiJSUzI1NiIsImtpZCI6Imk2bEdrM0ZaenhSY1ViMkMzbkVRN3N5SEpsW", + "accessTokenExpiresUtc": "2024-02-17T16:23:45Z", + "accessTokenType": "bearer" + } + protocol: HTTP + types: [ + "org.camaraproject.device-roaming-status-subscriptions.v0.roaming-status" + ] + config: { + "subscriptionDetail": { + "device": { + "phoneNumber": "+123456789", + } + }, + "subscriptionExpireTime": "2023-01-17T13:18:23.682Z", + "subscriptionMaxEvents": 5, + "initialEvent": true + } diff --git a/original/DeviceStatus/code/API_definitions/device-roaming-status.yaml b/original/DeviceStatus/code/API_definitions/device-roaming-status.yaml new file mode 100644 index 0000000000000000000000000000000000000000..7a0153d2ed1d8972397698fcd298c9c060987458 --- /dev/null +++ b/original/DeviceStatus/code/API_definitions/device-roaming-status.yaml @@ -0,0 +1,544 @@ +openapi: 3.0.3 +info: + title: Device Roaming Status + description: | + This API provides the API consumer with the ability to query device roaming Status + + # Introduction + + ## Roaming Status + API consumer is able to verify whether a certain user device is in roaming situation (or not). + + The verification of the roaming situation depends on the network's ability. Additionally to the roaming status, when the device is in roaming situation, visited country information could be returned in the response. + + ## Possible Use-Cases + Roaming status verification could be useful in scenario such as (not exhaustive): + - For regulatory reasons, where a customer may need to be within a certain jurisdiction, or out with others, in order for transactions to be authorized + - For security / fraud reasons, to establish that a customer is located where they claim to be + - For service delivery reasons, to ensure that the customer has access to particular service, and will not incur roaming charges in accessing them + + + ## Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + + * **Roaming** : Roaming status - `true`, if device is in roaming situation - `false` else. + + * **Country** : Country code and name - visited country information, provided if the device is in roaming situation. + + * **LastStatusTime** : This property specifies the time when the status was last updated. Its presence in the response indicates the freshness of the information, while its absence implies the information may be outdated or its freshness is uncertain. + + # API Functionality + + The API exposes following capabilities: + + ## Device roaming situation + + The endpoint `POST /retrieve` allows to get roaming status and country information (if device in roaming situation) synchronously. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device for which the roaming status should be returned from that phone number. If the phone number is used as the device identifier when querying in a multi-SIM scenario, the API may: + - respond with an error, or + - return a combined roaming status for the multi-SIM group as a whole, or + - return the roaming status for a single device in the multi-SIM group, which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + ## Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 1.0.0 + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceStatus + +servers: + - url: "{apiRoot}/device-roaming-status/v1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Roaming status retrieval + description: Operation to get device roaming status and country information (if roaming) synchronously +paths: + /retrieve: + post: + tags: + - Roaming status retrieval + summary: "Get the current roaming status and the country information" + description: Get the current roaming status and the country information + operationId: getRoamingStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - device-roaming-status:read + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusRequest" + required: true + responses: + "200": + description: Contains information about current roaming status + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/RoamingStatusResponse" + examples: + No-Country-Name: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 901 + countryName: [] + Single-Country-Code: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 262 + countryName: ["DE"] + Multiple-Country-Codes: + value: + lastStatusTime: "2024-02-20T10:41:38.657Z" + roaming: true + countryCode: 340 + countryName: ["BL", "GF", "GP", "MF", "MQ"] + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "503": + $ref: "#/components/responses/Generic503" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schemas: + RoamingStatusResponse: + type: object + required: + - roaming + properties: + lastStatusTime: + $ref: "#/components/schemas/LastStatusTime" + roaming: + $ref: "#/components/schemas/ActiveRoaming" + countryCode: + $ref: "#/components/schemas/CountryCode" + countryName: + $ref: "#/components/schemas/CountryName" + + LastStatusTime: + description: Last time that the associated device roaming status was updated + type: string + format: date-time + example: "2024-02-20T10:41:38.657Z" + + ActiveRoaming: + description: Roaming status. True, if it is roaming + type: boolean + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + CountryCode: + description: The Mobile country code (MCC) as an geographic region identifier for the country and the dependent areas. + type: integer + + CountryName: + description: The ISO 3166 ALPHA-2 country-codes of mapped to mobile country code(MCC). If there is mapping of one MCC to multiple countries, then we have list of countries. If there is no mapping of MCC to any country, then an empty array [] shall be returned.. + type: array + items: + type: string + + RoamingStatusRequest: + description: The request for retrieving the current roaming status for the requested device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Network issue diff --git a/original/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ac06e7e7f094e3849845ab350e8bcd716ff4dbc6 --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/connected-network-type-API-Readiness-Checklist.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for connected-network-type 0.1.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type.yaml](/code/API_definitions/connected-network-type.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type.feature](/code/Test_definitions/connected-network-type.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..3b9f14cf5c91f6fe6d184a7d8da7a758bf45c61c --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/connected-network-type-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for connected-network-type-subscriptions 0.1.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/connected-network-type-subscriptions.yaml](/code/API_definitions/connected-network-type-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/connected-network-type-subscriptions.feature](/code/Test_definitions/connected-network-type-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..9b88b214147b5cfaa5b37cc544d93c77b7d148e3 --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-API-Readiness-Checklist.md @@ -0,0 +1,24 @@ +# API Readiness Checklist + +Checklist for device-reachability-status 1.0.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-reachability-status.yaml](/code/API_definitions/device-reachability-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/device-reachability-status-User-Story.md](/documentation/API_documentation/device-reachability-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/device-reachability-status.feature](/code/Test_definitions/device-reachability-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | [see issue #258](https://github.com/camaraproject/DeviceStatus/issues/258) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story.md b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..6ad4c751c761baa12d65002a7aaf25c7decfe015 --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-User-Story.md @@ -0,0 +1,20 @@ +# Device Reachability Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the reachability status of a user's device, so that I can determine whether the device is reachable via SMS, data (mobile internet), or both, enabling better communication or service management decisions based on real-time device availability. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                                                                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                                                                    **Scope:** Order To Activate (OTA) - Get connectivity status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                                                                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the reachability status of a user's device | M | +| Ends when | The service provider returns the reachability status of the device with a timestamp when the status information was updated. In case of the device is reachable, additionally, the type of the connectivity (data, sms or both) is returned as well. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                    - Incorrect input data (e.g., malformed phone number).
                                                                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) diff --git a/original/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..f250882838480180bc2110a5948b11fd12c0ebae --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-reachability-status-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for device-reachability-status-subscriptions 0.7.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-reachability-status-subscriptions.yaml](/code/API_definitions/device-reachability-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-reachability-status-subscriptions.feature](/code/Test_definitions/device-reachability-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..e9d0cb68c7f74bfffa73750bbe4d0d373fb632fa --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-API-Readiness-Checklist.md @@ -0,0 +1,24 @@ +# API Readiness Checklist + +Checklist for device-roaming-status 1.0.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-roaming-status.yaml](/code/API_definitions/device-roaming-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/device-roaming-status-User-Story.md](/documentation/API_documentation/device-roaming-status-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions/device-roaming-status.feature](/code/Test_definitions/device-roaming-status.feature) | +| 9 | Test result statement | O | O | O | M | Y | [see issue #258](https://github.com/camaraproject/DeviceStatus/issues/258) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | + +(1) GSMA certified implementations of previous version by multiple operators (source: https://open-gateway.gsma.com/map as of 2025-03-11) + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story.md b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..605559aad78f50e8c137d358cc325cc070fe8070 --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-User-Story.md @@ -0,0 +1,21 @@ +# Device Roaming Status User Story + +| Item | Description | Support Qualifier | +|---------------------------|-------------|-------------------| +| Summary | As an enterprise application developer, I want to query the roaming status of a user's device, so that I can determine whether a device is in a foreign network and in which country it is located. This API can be used to identify fraud, ensure regulatory compliance, or enforce territorial restrictions on video and audio content. | M | +| Roles, Actor(s) and scope | **Roles:** Customer:Developer
                                                                    **Actors:** Application service providers (ASP), hyperscalers, application developers.
                                                                    **Scope:** Order To Activate (OTA) - Get roaming status of a device | M | +| NF Requirements | - | O | +| Pre-conditions | - The customer:developer has been successfully onboarded to the API platform of the service provider
                                                                    - The customer application has requested and received an access token with the required scope for the API | M | +| Begins when | The customer application server makes a POST request to retrieve the roaming status of a user's device | M | +| Ends when | The service provider returns the roaming status of the device with a timestamp when the status information was updated. In case of a roaming situation also the roaming country name and code shall be returned. | | +| Post-conditions | - | M | +| Exceptions | Several exceptions might occur during the API operations:
                                                                    - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                    - Incorrect input data (e.g., malformed phone number).
                                                                    - Not found: The phone number is not associated with a CSP customer account | M | + +# Linking a user story to API design + +Once we have the user story, the next step is to clarify the **data journey** in the context of the target and source systems we are integrating: +- Think about triggers for workflows: how and when does data need to be moved between the application and the service? +- Think about dependencies of data objects: does the data in underlying objects need to be regularly kept in sync with another system? +- Think about any parameters the user might need to configure or change. This is particularly important when building self-serve integrations for non-technical end users. +- Think about privacy by design: does any data represent sensitive information, and how can this be safely shared/stored according to regulation (e.g., anonymisation, tokenisation, zero-trust principles) + diff --git a/original/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..8c7dc01307f776a5fa3ac17af90cef97e26fb4fd --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/device-roaming-status-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,22 @@ +# API Readiness Checklist + +Checklist for device-roaming-status-subscriptions 0.7.0 in r2.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/device-roaming-status-subscriptions.yaml](/code/API_definitions/device-roaming-status-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions/device-roaming-status-subscriptions.feature](/code/Test_definitions/device-roaming-status-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceStatus/documentation/API_documentation/resources/README.MD b/original/DeviceStatus/documentation/API_documentation/resources/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceStatus/documentation/API_documentation/resources/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29.md new file mode 100644 index 0000000000000000000000000000000000000000..d9922c384eaf2a126f270b8c5063007354e19398 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-03-29.md @@ -0,0 +1,48 @@ +# Camara DeviceStatus meeting - MOM-2023-03-29 + +*March 29th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Mona Mokhber (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Robert Ludivic (Orange) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + - rewrite the issue to one time request + - start discussion +* [#24 Tag version 0.2.0](https://github.com/camaraproject/DeviceStatus/issues/24) + - 0.2.0 release branch is created but it should be protected => this issue can be closed +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) + - related to the PR about subscriptions: https://github.com/camaraproject/WorkingGroups/pull/173 . This issue should be discussed or modified after its approval. +* [#15 Update commonalities glossary with subproject relevant terms](https://github.com/camaraproject/DeviceStatus/issues/15) + - update with camelcase names (Rafal) +* [#14 Align error message with structure defined in the guideline](https://github.com/camaraproject/DeviceStatus/issues/14) + - Mona creates the PR, target 0.5.0-wip + +### Open PRs +* [#33 Update MAINTAINERS.MD](https://github.com/camaraproject/DeviceStatus/pull/33) + - needs owner review +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + - on hold + +## AOB +* Create 0.4.0 release branch (Akos) +* Further releases should be developed as proposed in Commonalities, using -wip in the version name during development of the next release + +* Next call will be on 12.04.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12.md new file mode 100644 index 0000000000000000000000000000000000000000..3d29fb7ff736047f8b1d45ef2f772a44b2df74d3 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-04-12.md @@ -0,0 +1,47 @@ +# Camara DeviceStatus meeting - MOM-2023-04-12 + +*April 12th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Mona Mokhber (Telefonica) +* Murat Karabulut (Deutsche Telekom) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#37 Create release 0.4.0](https://github.com/camaraproject/DeviceStatus/issues/37) + - Eric will create the release +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + - start discussion +* [#24 Tag version 0.2.0](https://github.com/camaraproject/DeviceStatus/issues/24) + - 0.2.0 release branch is created but it should be protected => this issue can be closed + - codeowners have no rights for branch protection (Akos will contact Herbert about it) +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) + - related to the PR about subscriptions: https://github.com/camaraproject/WorkingGroups/pull/173 . This issue should be discussed or modified after its approval. +* [#14 Align error message with structure defined in the guideline](https://github.com/camaraproject/DeviceStatus/issues/14) + +### Open PRs +* [#35 Errors definition alignment with guidelines](https://github.com/camaraproject/DeviceStatus/pull/35) + - additional approvals required +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + - on hold + +## AOB +* Next call will be on 26.04.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21.md new file mode 100644 index 0000000000000000000000000000000000000000..39d0bd3cfd9d2546d5fe32ae8577d083141ef0c7 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-06-21.md @@ -0,0 +1,44 @@ +# Camara DeviceStatus meeting - MOM-2023-06-21 + +*June 21st, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* AOB + + +### Open issues: + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Will be fixed in [PR31](https://github.com/camaraproject/DeviceStatus/pull/31) + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +Open issue: which type of connectivity is needed. +Input from Jorge: GSMA is already working on the use cases, which possible should be considered in CAMARA also. Decision: we wait until next DeviceStatus call. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is open + +### Open PRs +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + + +## AOB +* Create API roadmap draft => Akos +* Create Issue for documentation => Akos + +* Next call will be on 05.07.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05.md new file mode 100644 index 0000000000000000000000000000000000000000..8ed2cd4440dc0ccb40596df1f568fd593da88991 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-05.md @@ -0,0 +1,56 @@ +# Camara DeviceStatus meeting - MOM-2023-07-05 + +*July 5th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Mona Mokhber (Telefonica) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Will be fixed in [PR31](https://github.com/camaraproject/DeviceStatus/pull/31) + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +No input from GSMA available. The PR can be created, based on the discussions. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is open + +## Open PRs +* [#31 Adding notification/subscription for Device Status](https://github.com/camaraproject/DeviceStatus/pull/31) + +## API Roadmap +### Release 0.5.0 +* July-August 2023 +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) / +[PR#31](https://github.com/camaraproject/DeviceStatus/pull/31) + +### Release 0.6.0 +* September-Oktober 2023 +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + +## AOB + +* Next call will be on 19.07.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19.md new file mode 100644 index 0000000000000000000000000000000000000000..10d58dc44fe2d2fc8ea58a6349c0c6c3e4bab513 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-07-19.md @@ -0,0 +1,64 @@ +# Camara DeviceStatus meeting - MOM-2023-07-19 + +*July 19th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Masaharu Hattori (KDDI) +* Mona Mokhber (Telefonica) +* Rafal Artych (Deutsche Telekom) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR65](https://github.com/camaraproject/DeviceStatus/pull/65) is open. + +* [#52 Harmonize device object with QoD API](https://github.com/camaraproject/DeviceStatus/issues/52) +Has been fixed by [PR31](https://github.com/camaraproject/DeviceStatus/pull/31), the issue can be closed. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +No input from GSMA available. The PR can be created, based on the discussions. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) is closed, the issue can be closed too. + +## Open PRs +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + The goal is to merge the PR by the end of CW29. + +## API Roadmap +### Release 0.5.0 +* July-August 2023 +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* After [PR#65](https://github.com/camaraproject/DeviceStatus/pull/65) has been merged, the release can be created (Eric). + +### Release 0.6.0 +* September-Oktober 2023 +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) + +## AOB + +* New issue: How to handle mandatory and optional features of each API + * Definition of minimum implementation of a Camara API + * How can a provider inform the ASP/aggregator about not implemented features in advance of the API call? + * An issue in commonalities should be created +* Next call will be on 02.08.2023 11:00 CET + diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13.md new file mode 100644 index 0000000000000000000000000000000000000000..5c2b02f01596dc5d30bd9f7d4def1fab8176c72e --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-13.md @@ -0,0 +1,72 @@ + # Camara DeviceStatus meeting - MOM-2023-09-13 + +*September 13th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Prashant Sidana (E&) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR65](https://github.com/camaraproject/DeviceStatus/pull/65) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) + +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + The PR should be adapted when CloudEvents will be introduced => status delayed. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of the planned switch to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +* [#65 Add documentation](https://github.com/camaraproject/DeviceStatus/pull/65) + + +## AOB + +* New issue: How to handle mandatory and optional features of each API + * Definition of minimum implementation of a Camara API + * How can a provider inform the ASP/aggregator about not implemented features in advance of the API call? + * An issue in commonalities should be created (Prashant) +* New issue: Change notifications to be based on CloudEvents + The issue is linked to the related issues/PRs in Commonalities (add links). + The issue should also add missing event types for connectivity status. (after [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) has been merged.) + +* Next call will be on 27.09.2023 11:00 CET + diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27.md new file mode 100644 index 0000000000000000000000000000000000000000..9caa6d0d345febfc0e7c28541b8197f96c35889f --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-09-27.md @@ -0,0 +1,70 @@ + # Camara DeviceStatus meeting - MOM-2023-09-27 + +*September 27th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. This issue can be closed. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Based on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of switching to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 11.10.2023 11:00 CET + diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11.md new file mode 100644 index 0000000000000000000000000000000000000000..cc52e0c5cf05a3f623723a6575acb1edbc43fb8e --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-11.md @@ -0,0 +1,71 @@ +# Camara DeviceStatus meeting - MOM-2023-10-11 + +*October 11th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Noel Wirzius (Deutsche Telekom) +* Prashant Sidana (E&) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#71 Release plan&content](https://github.com/camaraproject/DeviceStatus/issues/71) +The upcoming releases were agreed as described below. This issue can be closed. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Depending on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) +Reviews are requested. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* The release is delayed because of switching to CloudEvents. +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 25.10.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25.md new file mode 100644 index 0000000000000000000000000000000000000000..a301d6d661d0d411434dee22008c2deab9b19d5b --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-10-25.md @@ -0,0 +1,65 @@ +# Camara DeviceStatus meeting - MOM-2023-10-25 + +*October 25th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#70 Info required : API understanding](https://github.com/camaraproject/DeviceStatus/issues/70) +The issue can be closed. + +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) + [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) is open. + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +Currently with the roaming status types, but it can be extended, when e.g. connectivity status info is added to the API. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Depending on [PR75](https://github.com/camaraproject/DeviceStatus/pull/75). + +* [#75 Added Notification management aligned with CloudEvents format](https://github.com/camaraproject/DeviceStatus/pull/75) +Reviews are requested. + +## API Roadmap + +### Release 0.5.0 +* September-October 2023 +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [#74 Align event-subscriptions with updated design guidelines based on CloudEvents](https://github.com/camaraproject/DeviceStatus/issues/74) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* [#57 Add documentation into API definition](https://github.com/camaraproject/DeviceStatus/issues/57) => [PR75](https://github.com/camaraproject/DeviceStatus/pull/75) +* After merging all PRs the first Releasecandidate should be created +### Release 0.6.0 +* November-December 2023 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 08.11.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08.md new file mode 100644 index 0000000000000000000000000000000000000000..5a7f52f880cee22b8178583de28c233816cc36fb --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-08.md @@ -0,0 +1,54 @@ +# Camara DeviceStatus meeting - MOM-2023-11-08 + +*November 8th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgreen (Ericsson) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) +* Sebastian Köller (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: + +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) is open. + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +[PR31](https://github.com/camaraproject/DeviceStatus/pull/31) introduced a generic subscription endpoint. +[PR69](https://github.com/camaraproject/DeviceStatus/pull/69) extends the API with connectivity related events. + +## Open PRs +* [#69 add /connectivity - endpoint to check the network status of a device](https://github.com/camaraproject/DeviceStatus/pull/69) +Update the PR with connectivity-events based on CloudEvents. Status: open for reviews. + +## API Roadmap + +### Release 0.5.0 +* November 2023 +* [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) +* [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) +* [#34 New Endtype Connectivity](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) +* [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) +* [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) +* After merging all PRs the first Releasecandidate should be created +### Release 0.6.0 +* Q1 2024 +* OIDC + +## AOB +* New issue to align with DG about security => Replace Client Credentials with OIDC (based on commonalities [PR57](https://github.com/camaraproject/Commonalities/pull/57)) +* Next call will be on 22.11.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22.md new file mode 100644 index 0000000000000000000000000000000000000000..f90b88674318feec599eb9432e78df291247698d --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-11-22.md @@ -0,0 +1,51 @@ +# Camara DeviceStatus meeting - MOM-2023-11-22 + +*November 22nd, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* API Roadmap +* AOB + + +## Open issues: +* [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) + A PR should be created. + +* [#81 enhance v0.4.1 to follow latest CAMARA guidelines](https://github.com/camaraproject/DeviceStatus/issues/81) + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +Almost all requirements have been implemented (except support for multiple devices), the issue should be closed. + + +## Open PRs +* + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the planned release content has been merged, the first release candidate should be created. +* Release content: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) + +## AOB +* Next call will be on 06.12.2023 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06.md new file mode 100644 index 0000000000000000000000000000000000000000..fc3f53f53e0127638040df94c3bfb3fe11ad9377 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2023-12-06.md @@ -0,0 +1,58 @@ +# Camara DeviceStatus meeting - MOM-2023-12-06 + +*December 6th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* Open Discussions +* API Roadmap +* AOB + + +## Open issues: +* [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + We agreed, that the issue can be implemented as proposed. + +* [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) +PR is open. + +* [#81 enhance v0.4.1 to follow latest CAMARA guidelines](https://github.com/camaraproject/DeviceStatus/issues/81) + +* [#17 Subscription Mode with new Eventtypes](https://github.com/camaraproject/DeviceStatus/issues/17) +Almost all requirements have been implemented (except support for multiple devices), the issue should be closed. + +## Open PRs +* [#87 Create release candidate 0.5.0-rc](https://github.com/camaraproject/DeviceStatus/pull/87) +The PR is blocked by [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + +## Open discussions +* + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the planned release content has been merged, the first release candidate should be created. +* Release content: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [#84 Minor corrections in Subscription model before release](https://github.com/camaraproject/DeviceStatus/issues/84) + * [#82 Create release candidate 0.5.0](https://github.com/camaraproject/DeviceStatus/issues/82) => [PR#87](https://github.com/camaraproject/DeviceStatus/pull/87) + +## AOB +* Next call will be on 20.12.2023 11:00 CET - However, when the 0.5.0-rc could be created earlier then this call should be skipped. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17.md new file mode 100644 index 0000000000000000000000000000000000000000..30ca43bc7a7209e4043305120cf6fa0fb0b30901 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-01-17.md @@ -0,0 +1,67 @@ +# Camara DeviceStatus meeting - MOM-2024-01-17 + +*January 17th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Ludovic Robert (Orange) +* Ming Hui Foo (Singtel) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open issues +* Open PRs +* Open Discussions +* API Roadmap +* AOB + + +## Open issues: +* [#97 Update response codes to string, following other CAMARA APIs](https://github.com/camaraproject/DeviceStatus/issues/97) + The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) +The issue should be implemented after releasing the 0.5.0. + +* [#94 Corrections needed to resolve linting errors](https://github.com/camaraproject/DeviceStatus/issues/94) + The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +## Open PRs +* [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + The PR is ready to be merged. + +## Open discussions +* [#98 Roaming Status - AgeOfInformation (or last_updated_timestamp)](https://github.com/camaraproject/DeviceStatus/discussions/98) + It should be converted to an issue to continue the discussion there. +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Planned release date: January 2024 +* Status: the release candidate 0.5.0-rc has been created. If no more bugs or findings in the 0.5.0-rc will be reported in the next 2 weeks, then the official release 0.5.0 can be created (no rc2 is necessary). +* Release content 0.5.0-rc: + * [~~#52 Harmonize device object with QoD API~~](https://github.com/camaraproject/DeviceStatus/issues/52) + * [~~#31 Adding notification/subscription for Device Status~~](https://github.com/camaraproject/DeviceStatus/pull/31) + * [~~#34 New Endtype Connectivity~~](https://github.com/camaraproject/DeviceStatus/issues/34) => [PR69](https://github.com/camaraproject/DeviceStatus/pull/69) + * [~~#74 Align event-subscriptions with updated design guidelines based on CloudEvents~~](https://github.com/camaraproject/DeviceStatus/issues/74) + * [~~#57 Add documentation into API definition~~](https://github.com/camaraproject/DeviceStatus/issues/57) + * [~~#84 Minor corrections in Subscription model before release~~](https://github.com/camaraproject/DeviceStatus/issues/84) + * [~~#82 Create release candidate 0.5.0~~](https://github.com/camaraproject/DeviceStatus/issues/82) => [PR#87](https://github.com/camaraproject/DeviceStatus/pull/87) +* Release content 0.5.0: + * [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + * New issue&PR to prepare the release + +## AOB +* Next call will be on 14.02.2024 11:00 CET +* Since the API is already in a mature status, a v1.0.0 should be targeted. => Create an issue to discuss about the process and the necessary to-do's. +* An issue for creation of the necessary feature file for testing should be created too. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14.md new file mode 100644 index 0000000000000000000000000000000000000000..d0515b7786dd71dc894b8fe269281c19ec5e7a33 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-14.md @@ -0,0 +1,82 @@ +# Camara DeviceStatus meeting - MOM-2024-02-14 + +*February 14th, 2024* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Jorge Garcia Hospital (Telefonica) +* Ludovic Robert (Orange) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * Renaming the POST endpoints according to the design guidelines. No discussion, can be merged after approvals. + +* [#109 fix: add missing "subscriptionId" in "RoamingStatus"-data for CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/109) + * No discussion, can be merged after approvals. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + +## Open issues: + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + * Is the information on 3GPP available at all? + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * No discussion, a PR should be created. + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#97 Update response codes to string, following other CAMARA APIs](https://github.com/camaraproject/DeviceStatus/issues/97) + * The corresponding PR is open: [#95 Corrections resolving linting errors](https://github.com/camaraproject/DeviceStatus/pull/95) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* [#105 v0.5.0 - Difference between "subscriptionExpireTime" & "expiresAt" in "SubscriptionInfo"](https://github.com/camaraproject/DeviceStatus/discussions/105) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#98 Roaming Status - AgeOfInformation (or last_updated_timestamp)](https://github.com/camaraproject/DeviceStatus/discussions/98) + * An issue [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) has been created, the discussion can be closed. +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Status: release created on 31.01.2024 + +### Release 0.6.0 +* Planned release date: tbd +* Status: wip +* Content: + + +## AOB +* Next call will be on 28.02.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created too. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28.md new file mode 100644 index 0000000000000000000000000000000000000000..fa62ba2ccc66da5a8f32d80fb483789c5ac9acdd --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-02-28.md @@ -0,0 +1,88 @@ +# Camara DeviceStatus meeting - MOM-2024-02-28 + +*February 28th, 2024* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * Renaming the POST endpoints according to the design guidelines. + * No discussion, can be merged after approvals. + +* [#109 fix: add missing "subscriptionId" in "RoamingStatus"-data for CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/109) + * No discussion, can be merged after approvals. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + +## Open issues: + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * Same issue exists in Device Location + * Should be addressed in Commonalities + +* [#116 subscriptionExpireTime is declared as "required" in the subscription-ends - note, but is optional currently](https://github.com/camaraproject/DeviceStatus/issues/116) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* **[#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114)** +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.0 +* Status: release created on 31.01.2024 + +### Release 0.6.0 +* Planned release date: tbd +* Status: wip +* Content: A proposal for the content should be created (Ákos) + + +## AOB +* Next call will be on 13.03.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13.md new file mode 100644 index 0000000000000000000000000000000000000000..002a67d8ba10e75b9c98eae81cbf3305b26f40d5 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-13.md @@ -0,0 +1,112 @@ +# Camara DeviceStatus meeting - MOM-2024-03-13 + +*March 13th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Ludovic Robert (Orange) +* Maximilian Laue (Deutsche Telekom) +* Quanain Meghjee (Vonage) +* Rafal Artych (Deutsche Telekom) +* Sachin Kumar (Vodafone) +* Toyeeb Rehmann (GSMA) + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs + +* [#127 Updated in-line documentation for Roaming to clarify that country information can optionally be returned in the response](https://github.com/camaraproject/DeviceStatus/pull/127) + +* [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * No discussion + * Reviews are missing. + +* [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + * Should be first clarified in Commonalities: camaraproject/Commonalities#153 + +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + * The fix for the typo should be covered in a separate PR. + +* [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + * The PR has been merged accidentally, but then the change has been reverted. This PR should be merged after the bugfix release v0.5.1 has been created. + * A new PR should be opened. + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + * An issue in Commonalities has been opened camaraproject/DeviceLocation#149 + +## Open issues: + +* [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + * Split the current API into 4 different APIs + +* [#124 When roaming status is true, is it mandatory to return both countryCode and countryName?](https://github.com/camaraproject/DeviceStatus/issues/124) + +* [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +* [#119 How can a provider inform the ASP/aggregator about not implemented features in advance of the API call](https://github.com/camaraproject/DeviceStatus/issues/119) + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * The corresponding PR is open: [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * A new PR should be created see [#111 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/111) + + + +## Open discussions +* [#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.x +* The release v0.5.0 was created on 31.01.2024 +* The bugfix release 0.5.1 is planned [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +### Release 0.6.0 +* Planned release date: tbd +* Content: + * [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * ?? [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + + +## AOB +* Next call will be on 27.03.2024 11:00 CET +* An issue for creation of the necessary feature file for testing should be created. diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27.md new file mode 100644 index 0000000000000000000000000000000000000000..5e7d8fab6aabeaf77a8d3ba1ac9de46aed23dc4f --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-2024-03-27.md @@ -0,0 +1,117 @@ +# Camara DeviceStatus meeting - MOM-2024-03-27 + +*March 27th, 2024* + +## Attendees + +* Aishwarya Javkhedkar (Comviva) +* Ankita () +* Akos Hunyadi (Deutsche Telekom) +* Fernando Prado Cabrillo (Telefonica) +* Joachim Dahlgren (Ericsson) +* Quanain Meghjee (Vonage) +* Sachin Kumar (Vodafone) + + +DeviceStatus minutes: [https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/DeviceStatus/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Open Discussions +* API Roadmap +* AOB + + +## Open PRs + +* [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + * PR was recreated after accedentally merging too early + * Planned release v0.6.0 + +* [#129 fix: change INVALID_INPUT for INVALID_ARGUMENT according to guidelines](https://github.com/camaraproject/DeviceStatus/pull/129) + * Review in progress + * Planned release v0.5.1 + +* [#127 Updated in-line documentation for Roaming to clarify that country information can optionally be returned in the response](https://github.com/camaraproject/DeviceStatus/pull/127) + * Review in progress + * Planned release v0.5.1 + +* [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * No discussion + * Reviews are missing. + +* [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + * Should be first clarified in Commonalities: camaraproject/Commonalities#153 + +* [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * No discussion + * Reviews are missing. + * Planned release v0.6.0 + +* [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + * The enums for event-types include dots which causes problems at the code generation (Java) at DT. + * Additional feedback from dev teams would be helpful to priotize the issue. + * A possible change in the design guideline could be a solution. + * The PR has been marked as draft until an agreed solution is ellaborated. + * An issue in Commonalities has been opened camaraproject/DeviceLocation#149 + +## Open issues: + +* [#130 What should the API return if more than one device identifier is sent and they don't belong to the same device?](https://github.com/camaraproject/DeviceStatus/pull/130) + +* [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + * Split the current API into 4 different APIs + +* [#124 When roaming status is true, is it mandatory to return both countryCode and countryName?](https://github.com/camaraproject/DeviceStatus/issues/124) + +* [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +* [#119 How can a provider inform the ASP/aggregator about not implemented features in advance of the API call](https://github.com/camaraproject/DeviceStatus/issues/119) + +* [#117 Send a CloudEvent when DELETE /subscriptions/{subscriptionId}](https://github.com/camaraproject/DeviceStatus/issues/117) + * The corresponding PR is open: [#121 feat: add termination reason when subscription deleted](https://github.com/camaraproject/DeviceStatus/pull/121) + +* [#115 /Connectivity API there is no indication for which particular subscriber event (DATA/SMS)](https://github.com/camaraproject/DeviceStatus/issues/115) + +* [#110 Request for Addition of "last_updated_timestamp" Field in CAMARA DeviceStatus API](https://github.com/camaraproject/DeviceStatus/issues/110) + * The name should correlate with similar properties at other APIs + +* [#107 Use simple string for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/issues/107) + * The corresponding PR is open: [#108 feat: use simple String for "type" in CloudEvent](https://github.com/camaraproject/DeviceStatus/pull/108) + +* [#104 Include x-correlator heade](https://github.com/camaraproject/DeviceStatus/issues/104) + * The corresponding PR is open: [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + +* [#102 Clarify API readiness status for v1.0.0](https://github.com/camaraproject/DeviceStatus/issues/102) + +* [#96 Path update per Design Guideline](https://github.com/camaraproject/DeviceStatus/issues/96) + * The corresponding PR is open: [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + + + +## Open discussions +* [#114 Test Data : Device Status](https://github.com/camaraproject/DeviceStatus/discussions/114) +* [#100 Granularity of the Test Definition feature file](https://github.com/camaraproject/DeviceStatus/discussions/100) +* [#89 Multi-Operator Demo Test Discussion](https://github.com/camaraproject/DeviceStatus/discussions/89) +* [#72 CAMARA Compliant: Expose all end points](https://github.com/camaraproject/DeviceStatus/discussions/72) +* [#48 Need support](https://github.com/camaraproject/DeviceStatus/discussions/48) + +## API Roadmap + +### Release 0.5.x +* The release v0.5.0 was created on 31.01.2024 +* The bugfix release 0.5.1 is planned [#122 Bugfix release v0.5.1](https://github.com/camaraproject/DeviceStatus/issues/122) + +### Release 0.6.0 +* Planned release date: tbd +* Content: + * [#131 Update device-status.yaml](https://github.com/camaraproject/DeviceStatus/pull/131) + * [#112 include x-correlator and fix typo in 400 error code](https://github.com/camaraproject/DeviceStatus/pull/112) + * [#123 Adding configuration for Github Actions with linting ruleset](https://github.com/camaraproject/DeviceStatus/pull/123) + * ?? [#125 Separate endpoints into different APIs](https://github.com/camaraproject/DeviceStatus/pull/125) + + +## AOB +* Next call will be on 10.04.2024 11:00 CET diff --git a/original/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12.md b/original/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12.md new file mode 100644 index 0000000000000000000000000000000000000000..78fabc8e3e85f060d1a8ba29b1610523b441195e --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/MoM-DST-2022-12-12.md @@ -0,0 +1,35 @@ +# Meeting Minutes: Device Status WG +## Date: 12th December 2022 +## Attendees +- Eric Murray / Vodafone +- Sachin Kumar / Vodafone +- Ludovic Robert / Orange +- Joachim Dahlgren / Ericsson +- Mona Mokhber / Telefonica +## Pull Requests +- PR #8: Add documentation / DT + + It was agreed that: + - Final reviews of this PR should be undertaken this week + - Any comments to be raised by end of Friday 16th December, otherwise it will be approved +- PR #9: v0.3.0 based on Telefónica proposal / Telefonica + + It was agreed that: + - Outstanding issues / PRs in the Commonalities WG ([PR #68](https://github.com/camaraproject/WorkingGroups/pull/68), [Issue #101](https://github.com/camaraproject/WorkingGroups/issues/101), [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105)) need to be closed before this proposal can be progressed + - A separate API per status type (in this case, roaming status) was the best approach, and new APIs should be introduced for additional statuses (e.g. device connectivity state) + - If additional roaming status information was to be added (e.g. visited country, or PLMN ID), this should be implemented as additional paths to support different client access rights via scopes +## Issues +- Issue #6: Issues, branches, pull requests - cleaning up + - Issue closed +- Issue #7: Meetings ? + - Agreed to keep open until Noel has scheduled ongoing bi-weekly meetings +- Issue #2: Roaming Status API Proposal + - This was the original issue raised in the Commonalities WG, and now transferred to Device Status WG + - Agreed to revisit once PR #9 is resolved + - Link to original proposal is broken. Eric to copy over original proposal to Device Status WG and fix link. +- Issue #10: Telefonica proposal post MWC + - Issue raised to introduce PR #9 (discussed above). Can be used to raise questions about the proposal. +## Discussions +- None +## AOB +- Ongoing meetings to be scheduled by Noel. Anyone wishing to join should subscribe to the [mailing list](https://lists.camaraproject.org/g/sp-dst). diff --git a/original/DeviceStatus/documentation/MeetingMinutes/README.MD b/original/DeviceStatus/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceStatus/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceStatus/documentation/SupportingDocuments/README.MD b/original/DeviceStatus/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceStatus/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone.md b/original/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone.md new file mode 100644 index 0000000000000000000000000000000000000000..a7fc4d67dffe8f6606448fe67cf01a93ad5459f2 --- /dev/null +++ b/original/DeviceStatus/documentation/SupportingDocuments/Roaming_API_Proposal_-_Vodafone.md @@ -0,0 +1,31 @@ +# Roaming Status API +Device (i.e. UE) status indications are an important family of APIs where the API consumer is not the device itself. One status indication that has several use cases is the roaming status of the device. Roaming in this context is defined as being connected to a network other than the subscriber's home network, and so would include national roaming (where allowed) in addition to international roaming. + +For example, such information could be useful in the following scenarios: +- For regulatory reasons, where a customer may need to be within a certain jurisdication, or outwith others, in order for transactions to be authorised +- For security / fraud reasons, to establish that a customer is located where they claim to be +- For service delivery reasons, to ensure that the customer has access to particular services, and will not incur roaming charges in accessing them + +### Inputs +- The target UE whose roaming status is required should be explicitly identified by its GPSI (MSISDN or External Identifier). It is not expected that the UE itself will call this API, and hence OIDC will not identify the target UE. +- When a boolean indication of whether or not a UE is in a specific country, the ISO country code for that country must be provided + + +### Outputs +It is proposed that a roaming status API is able to provide the following information to API consumers: +- A boolean indicator of roaming state (i.e. roaming / not roaming) +- if roaming, an indicator of whether that is national or international roaming (i.e. does the ISO country code for the home MCC equal that of the visited MCC or not) +- The ISO country code corresponding to the MCC of the network the device is currently connected to or, where the MCC does not have a corresponding ISO country code, the MCC itself +- The full PLMN of the network that the device is currently connected to (MCC + MNC) +- A boolean indicator of whether a device is in a specified country (specified by ISO country code) + +### Notifications +It should be possible for the API caller to be notified of any change in roaming status + +## Implementation +UE roaming status information can be obtained either directly from the HSS, or via the SCEF/NEF "ROAMING_STATUS" monitoring capability + +## Notes +- API consumers would be able to access all or only some of this information, depending on their level of authorisation +- Some lucky countries (e.g. UK, USA, India, China) have multiple MCCs, hence care must be taken when deciding roaming status on the basis of the visited network MCC +- A very few MCCs are shared between multiple countries (specifically, countries with different ISO country codes - for example, French DROMs or British Crown Dependencies). In these cases, the ISO country code needs to be determined from the full visited network PLMN. diff --git a/original/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis.md b/original/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis.md new file mode 100644 index 0000000000000000000000000000000000000000..2491967645ec1480383198019f4e40303b32eb08 --- /dev/null +++ b/original/DeviceStatus/documentation/SupportingDocuments/decision-support-1-or-2-apis.md @@ -0,0 +1,136 @@ +# Decision supporting document for the discussion 1 or 2(n) APIs + +## Current situation +The device-status API has 1 endpoint: /roaming. +There is a need to add new functionalities. At first 2 new endpoints: to get the connectivity status and to subscribe for status-events. +Later other functionalities will follow. + +### Option 1 +Logically related endpoints are generally within 1 API, with 1 basepath. In special cases (e.g. compliance) splitting is possible. +Example: +{apiRoot}/device-status/v0/roaming +{apiRoot}/device-status/v0/connectivity +{apiRoot}/device-status/v0/subscriptions + +### Option 2 +Each device status subtype is handled in a separate API with different basepaths building an API-family. +Example: +API #1 +{apiRoot}/device-roaming-status/v0/roaming +{apiRoot}/device-roaming-status/v0/subscriptions + +API #2 +{apiRoot}/device-connectivity-status/v0/connectivity +{apiRoot}/device-connectivity-status/v0/subscriptions + + +## Criterias + +### 1. API usage - client view + +Aspects of finding and using the API(s) for a specific use case of a client. + +**Separate basepath** + +Pros: +- For a use case with a single area of interest (e.g. only roaming status is needed) a specific small API might be easier to be found and used + +Cons: +- For more complex use cases many device status-APIs are needed (find, subscribe, integrate, etc.) + + +**Common basepath** + +Pros: +- For a use case with multiple areas of interest or the intention to extend the usage later a combined API with all device status related information is more comfortable +- Only one API onboarding +- In this very specific context, the 2 functions are very close. + +Cons: +- If only one specific status is needed, then it might take longer to find the right information + + +### 2. Service development and operation - provider view +Aspects of the service implementation, testing, and operation on the provider side. + +**Separate basepath** + +Pros: +- Independent implementation and testing of the different status functionalities +- Fine-grade billing, scaling and monitoring is possible (however more effort) + +Cons: +- Extra effort is needed to prevent doubled code +- More overhead on developing and operating multiple services + +**Common basepath** + +Pros: +- Efficient development (especially when all status information can be gathered from the same southbound service) +- Model generation performed once + +Cons: +- If different southbound services are used the service gets more complex +- It might lead to partial implementations when there is an interest in some of the use cases and not the others + + +### 3. API maintenance & releasing - Camara view +Aspects of maintenance (add, delete, change functionality) and releasing (versioning, release planning, etc.) + +**Separate basepath** + +Pros: +- A simple service is easier to maintain and release +- Version changes are tightly related to the API functionality + +Cons: +- The overall effort (discussions, YAML work, etc.) for the API family is higher +- Additional synchronization within the API family is necessary (using common types could help) + +**Common basepath** + +Pros: +- Bigger releases with higher value +- Easy to add a new endpoint to an existing API + +Cons: +- Longer release cycles (more content, more discussions) +- Introducing changes/updates in one of the endpoints will result a version change affecting other unrelated endpoints (specially when they are not backward compatible) + + +### 4. Harmonization - technical view +Aspects of industry best practice, generic design guidelines and harmonization with other Camara APIs. + +**Some examples** +- 3GPP APIs are simple on the path level (collection and collection\\), inside the requests/responses many subtypes are used +- TM-Forum APIs contain multiple different endpoints related to the API theme +- Camara APIs don't show a clear picture (range from very simple to "monster" APIs) + +**Separate basepath** + +Pros: +- Small API and microservice with very limited responsibility (however 1 microservice can implement multiple APIs also) + +Cons: +- Atomic APIs with very limited scopes are not typical + +**Common basepath** + +Pros: +- + +Cons: +- + +## Preference + +| Company | Preference | +| ------- | ---------- | +| Orange | Slight preference for one API with 2 resources but not a 'structral' point for us for this API. | +| Vodafone | Based on the information shared at https://github.com/camaraproject/WorkingGroups/discussions/218 against different other aspects, our preference is to have separate APIs for each status (Roaming/Connectivity). | +| Deutsche Telekom | We prefer the solution with a common basepath (1 API), however in specific cases a separation is conceivable | +| Telfónica | Our preference is to have separate APIs for different types of status | + + + + diff --git a/original/DeviceSwap/README.md b/original/DeviceSwap/README.md new file mode 100644 index 0000000000000000000000000000000000000000..aa4a5e86da381dbd7b2cf885279538a3b1b26cc3 --- /dev/null +++ b/original/DeviceSwap/README.md @@ -0,0 +1,54 @@ + + + + + + + + + +# DeviceSwap + +Incubating API Repository to evolve and maintain the definitions and documentation of DeviceSwap Service API(s) within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ijLe) + +## Scope +* Service APIs for “Device Swap” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * understand if the MSISDN has had a change of device in the last 30 days. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: July 2024 +* * Incubating stage since: June 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/DeviceSwap/releases/tag/r3.2) (Fall25), with the following API versions: + * **device-swap v1.0.0** + [[YAML]](https://github.com/camaraproject/DeviceSwap/blob/r3.2/code/API_definitions/device-swap.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/DeviceSwap/r3.2/code/API_definitions/device-swap.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/DeviceSwap/r3.2/code/API_definitions/device-swap.yaml) +* The latest public release is always available here: https://github.com/camaraproject/DeviceSwap/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/DeviceSwap/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/DeviceSwap/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Every 4 weeks Thursday at 7:30 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/hDze) + * [Minutes archive](https://lf-camaraproject.atlassian.net/wiki/x/5VPe) before May 2025 + +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceSwap/code/API_definitions/device-swap.yaml b/original/DeviceSwap/code/API_definitions/device-swap.yaml new file mode 100644 index 0000000000000000000000000000000000000000..1985d9d5a111f9d230b48df359d5adb456db7f12 --- /dev/null +++ b/original/DeviceSwap/code/API_definitions/device-swap.yaml @@ -0,0 +1,512 @@ +openapi: 3.0.3 +info: + title: Device Swap + description: | + This API allows to check the last time that the phone (device) - phone number association has changed + + # Introduction + + The Device Swap API performs real-time checks on the last Device Swap event, providing real-time information about whether the SIM card associated with a user's phone number has been transferred to a different physical device. + + Device Swap information can be invaluable for enhancing security, fraud detection, and ensuring compliance with regulatory requirements in various applications, apart from providing useful information of device upgrade trends in user segments. + + This API is used by an application to get information about a mobile line's latest Device Swap date. It can be easily integrated and used through this secured API and allows API consumers to get this information in an easy and secured way. The API provides management of 2 endpoints answering 2 distinct questions: + + * When did the last Device Swap occur? + * Has a Device Swap occurred during the last n hours? + + # Relevant terms and definitions + + **Device Swap:** A Device Swap is a process in which the association between a user's mobile phone number (MSISDN) and a device (IMEI) is created for the first time or changes for any reasons. + + # API Functionality + + The Device Swap API provides a programmable interface for developers and other users (capabilities consumers) to request the last date of a device swap performed on the mobile line, or, to check whether a device swap has been performed during a past period. + + The API provides 2 operations: + + - POST retrieve-date: Provides timestamp of latest device swap, if any, for a given phone number. + - If no swap has been performed and the network operator supports unlimited DeviceSwap monitoring timeframe, the API will return the first phone number usage in a device (the timestamp of the first time that the phone number was connected to the network, it is, the first time that the SIM is installed in a device). + - If the latest device swap date (or the first phone number usage, if no device swap) cannot be communicated due to local regulations (or Network Operator internal privacy policies) preventing the safekeeping of the information for longer than the stated period, a `null` value will be returned. Optionally, a `monitoredPeriod` could be provided to indicate monitored time frame (in days) supported by the Network Operator. In this case the response must be treated as "there were no device swap events during 'monitoredPeriod'. Either the parameter is optional, it is recommended to support it in DeviceSwap implementations. + - POST check: Checks if device swap has been performed during a past period (defined in the request with 'maxAge' attribute) for a given phone number, the API will return boolean response (true/false), indicating that the device has been swapped or not in the specified period. In case the phone number has never been installed in a device, or no data is available in the operators records (e.g. database error), API will return a 422 error. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API. There is 2 ways to retrieve it depending on the authorization flow used: + - When the API is invoked using a two-legged access token, the phone number will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the phone number will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the phoneNumber cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the phoneNumber can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/DeviceSwap + +servers: + - url: '{apiRoot}/device-swap/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Retrieve Device Swap Date + description: Receive the last date in which the device of the end-user was swapped + - name: Check Device Swap + description: Validate if the SIM of the end-user has been installed in a different device during a past period +paths: + /retrieve-date: + post: + tags: + - Retrieve Device Swap Date + summary: Get last device swap date + description: Get timestamp of last device swap for a mobile user account provided with phone number. + operationId: retrieveDeviceSwapDate + security: + - openId: + - device-swap + - openId: + - device-swap:retrieve-date + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a device swap date request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateDeviceSwapDate" + examples: + RETRIEVE_3LEGS: + $ref: "#/components/examples/RETRIEVE_3LEGS" + RETRIEVE_2LEGS: + $ref: "#/components/examples/RETRIEVE_2LEGS" + required: true + responses: + "200": + description: Contains information about Device swap change + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceSwapInfo" + examples: + RETRIEVE_DATE: + $ref: "#/components/examples/RETRIEVE_DATE" + RETRIEVE_MONITORED_PERIOD: + $ref: "#/components/examples/RETRIEVE_MONITORED_PERIOD" + RETRIEVE_MONITORED_NULL: + $ref: "#/components/examples/RETRIEVE_MONITORED_NULL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + /check: + post: + tags: + - Check Device Swap + summary: Check last device swap date + description: Check if device swap has been performed during a past period + operationId: checkDeviceSwap + security: + - openId: + - device-swap + - openId: + - device-swap:check + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + description: | + Create a check device swap request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateCheckDeviceSwap" + examples: + CHECK_3LEGS: + $ref: "#/components/examples/CHECK_3LEGS" + CHECK_2LEGS: + $ref: "#/components/examples/CHECK_2LEGS" + responses: + "200": + description: Returns whether a device swap has been performed during a past period + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckDeviceSwapInfo" + "400": + $ref: "#/components/responses/Generic400Check" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + DeviceSwapInfo: + type: object + required: + - latestDeviceChange + properties: + latestDeviceChange: + type: string + format: date-time + description: Timestamp of latest device swap performed. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + monitoredPeriod: + type: integer + description: Timeframe in days for device change supervision for the phone number. It could be valued in the response if the latest Device swap occurred before this monitored period. + example: 120 + CreateDeviceSwapDate: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + CreateCheckDeviceSwap: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + maxAge: + type: integer + example: 240 + description: | + Period in hours to be checked for device swap. + format: int32 + minimum: 1 + maximum: 2400 + default: 240 + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+34666111333' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + CheckDeviceSwapInfo: + type: object + required: + - swapped + properties: + swapped: + type: boolean + description: Indicates whether the device has been swapped during the period within the provided age. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic400Check: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: phone number is not included in the request (in case of 2-legged) or the phone number identification cannot be derived from access token (in 3-legged) + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. + examples: + RETRIEVE_DATE: + summary: Lastest Device swap date is send back + value: + latestDeviceChange: 2024-09-18T07:37:53.471829447Z + RETRIEVE_MONITORED_NULL: + summary: Only null value is retrieved + value: + latestDeviceChange: null + RETRIEVE_MONITORED_PERIOD: + summary: null is send back for the date but a monitoredPeriod is provided + value: + latestDeviceChange: null + monitoredPeriod: 120 + CHECK_2LEGS: + summary: Check request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + maxAge: 120 + CHECK_3LEGS: + summary: Check request with 3-legged access tokens + value: + maxAge: 120 + RETRIEVE_2LEGS: + summary: Retrieve request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + RETRIEVE_3LEGS: + summary: Retrieve request with 3-legged access tokens + value: + {} diff --git a/original/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist.md b/original/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..4c4524df506e15a30d0af8131f23aadbdbb19bae --- /dev/null +++ b/original/DeviceSwap/documentation/API_documentation/device-swap-API-Readiness-Checklist.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for device-swap v1.0.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                    public | stable
                                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](code/API_definitions/device-swap.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v1.0.0 | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/device-swap.yaml) | +| 6 | User stories | O | O | O | M | Y | [check](/documentation/API_documentation/device-swap_check_User_Story.md) [retrieve](/documentation/API_documentation/device-swap_retrieve_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [check](/code/Test_definitions/device-swap-checkDeviceSwap.feature) [retrieve](/code/Test_definitions/device-swap-retrieveDeviceSwapDate.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [check](/code/Test_definitions/device-swap-checkDeviceSwap.feature) [retrieve](/code/Test_definitions/device-swap-retrieveDeviceSwapDate.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue [#68](https://github.com/camaraproject/DeviceSwap/issues/68) | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166764/DeviceSwap+API+description) | + +(*) If you encounter issues with the provided test files (.feature), please create an issue in the API Sub-Project to signal these issues so they can be fixed in a patch release. + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story.md b/original/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..0597786c3be3476facead9b7ee44a0b5b5db7d8d --- /dev/null +++ b/original/DeviceSwap/documentation/API_documentation/device-swap_check_User_Story.md @@ -0,0 +1,11 @@ +# Device Swap Check API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check if a device swap has occurred within a specified period for a user's mobile number so that I can enhance security measures against account takeover fraud. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                                    **Scope:**
                                                                    - Checks if a device swap has occurred within a specified period for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:

                                                                    1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                                    2. The ASP:BusinessManager has successfully subscribed to the Device Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                                                    3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                                                    4. The ASP:User performs an authorization request to CSP
                                                                    5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                                    6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Device Swap API, providing the phone number and the desired period to check for device swaps. This request could be done via (or not) the Channel Partner.
                                                                      **Ends when:** The CSP's Device Swap server responds indicating whether a Device Swap has been performed within the specified period. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the End-User's line, based on the Device Swap information. | +| ***Exceptions*** | Several exceptions might occur during the Device Swap API operations
                                                                      - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                                                      - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| diff --git a/original/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story.md b/original/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..ede338eabba07224ce929e8e902b90a63ab71f15 --- /dev/null +++ b/original/DeviceSwap/documentation/API_documentation/device-swap_retrieve_User_Story.md @@ -0,0 +1,11 @@ +# Device Swap Retrieve API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the last device swap date for a user's mobile number so that I can enhance security measures against account takeover fraud. | +|***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                                      **Scope:**
                                                                      - Retrieves the timestamp of the last device swap event for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                      1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                                      2. The ASP:BusinessManager has successfully subscribed to the Device Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                                                      3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                                                      4. The ASP:User performs an authorization request to CSP
                                                                      5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                                      6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the Device Swap API, including the phone number provided by the End-User in the ASP:User.
                                                                        **Ends when:** The CSP's Device Swap server responds with the timestamp of the last device swap event, or the first SIM installation date if no device swap has occurred. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the End-User's line, based on the Device Swap information. | +| ***Exceptions*** | Several exceptions might occur during the Device Swap API operations
                                                                        - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                                                        - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).
                                                                        - Not able to provide: Legal restrictions or data retention policies preventing the retrieval of the requested information.| diff --git a/original/DeviceSwap/documentation/MeetingMinutes/README.MD b/original/DeviceSwap/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceSwap/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceSwap/documentation/SupportingDocuments/README.MD b/original/DeviceSwap/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceSwap/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceVisitLocation/README.md b/original/DeviceVisitLocation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..dd25d4c4593eddc7418a338aac60196dbc95eb4a --- /dev/null +++ b/original/DeviceVisitLocation/README.md @@ -0,0 +1,41 @@ + + + + + + + + + +# DeviceVisitLocation + +Sandbox API Repository to describe, develop, document, and test the DeviceVisitLocation Service API(s), working closely together with MostFrequentLocation. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQCICQ) + +## Scope + +* Service API(s) “DeviceVisitLocation” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * query the visit locations of a device during a certain time period. +* Describe, develop, document, and test the API(s) +* Started: May 2024 (originally as part of LocationInsights, own repository since July 2025) + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly, Thursday, 09:00 CEST (07:00 UTC) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99479758031?password=c705dd6f-a1c5-44e4-af97-331a18395fb8) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/XjPe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/DeviceVisitLocation/code/API_definitions/device-visit-location.yaml b/original/DeviceVisitLocation/code/API_definitions/device-visit-location.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e67c3fd64339d3694426f6953dabbe4fd0512084 --- /dev/null +++ b/original/DeviceVisitLocation/code/API_definitions/device-visit-location.yaml @@ -0,0 +1,772 @@ +--- +openapi: 3.0.3 +info: + title: Device Visit Location + description: > + The Device Visit Location API provides customers with the ability + to query the visit locations of a device during a certain time period. + + # Introduction + + This API can return the visited location of a device at a certain time, and the visited location is returned as a list of geoCode objects. + + This API can be used in the following scenarios.\ + + **Anti fraud**: for some scenarios involving high-risk financial operations (such as cross-border transfers, large investments, etc.), by monitoring changes in the location visited by mobile phone numbers, potential fraudulent behavior can be detected in advance. For example, when a user usually only operates in a few provinces within the country, but suddenly has access records from overseas or unfamiliar high-risk provinces, and there are also signs of abnormal fund flow, preventive measures can be taken quickly.\ + + **Identity verification**: In the financial field, when users perform high-risk operations such as large transfers or changing important account information, in addition to conventional verification methods such as passwords and verification codes, identity verification can also be carried out by combining their phone number with the province they recently visited.\ + + **Remote abnormal operation detection**: For the account security management of e-commerce platforms, when users perform login, password modification, payment and other operations, they can use this api to detect whether there are abnormal operations in remote locations. + + # Relevant terms and definitions + + * **Device**: A device refers to any physical entity that can connect to a network and participate in network communication. + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier (not supported for this API version) assigned by the mobile network operator for the device. + * **geoCode**: An object with the following attributes: + - **countryCode**: The code of the country.Following the `ISO 3166 ALPHA-2` standard. + - **codeType**: The type of code, such as "PostlCode". + - **codeValue**: The actual value of the code. + # API Functionality + + Once the API Consumer provides the device infomation and specifies the time window, the API queries the relevant data. The data is retrieved from the stored information within the selected time window. The result is returned as a list of geoCode objects representing the visited locations. + + ## Detailed Explanation of GeoCode Object + + **CountyCode**: This is a string type field used to specify the country code where the location is located. Following the `ISO 3166 ALPHA-2` standard, for example, "CN" represents China, "US" represents the United States, etc. On a global scale, this code ensures accurate differentiation of different countries and is an important foundational information for positioning, helping to quickly filter and identify location data for specific countries in cross-border business or data analysis.\ + + **codeType**: String type, used to specify the geographic encoding type used, with a fixed value of `PostlCode` in the current version. This field is designed to facilitate future expansion for different geographic coding systems, allowing capability providers to select the appropriate coding type for return based on actual situations.\ + + **codeValue**: String type, representing the specific encoding value of the corresponding codeType. For example, when codeType is `Postal Code`, codeValue may be a postal code similar to "100000". It, together with the countryCode and codeType, forms a complete location identifier that accurately points to a specific geographic area. + + # Identifying a device from the access token + + This specification defines the `device` object field as optional in API requests, specifically in cases where the API is accessed using a 3-legged access token, and the device can be uniquely identified by the token. This approach simplifies API usage for API consumers by relying on the device information associated with the access token used to invoke the API. + + ## Handling of device information: + + ### Optional device object for 3-legged tokens: + + - When using a 3-legged access token, the device associated with the access token must be considered as the device for the API request. This means that the device object is not required in the request, and if included it must identify the same device, therefore **it is recommended NOT to include it in these scenarios** to simplify the API usage and avoid additional validations. + + ### Validation mechanism: + + - The server will extract the device identification from the access token, if available. + + - If the API request additionally includes a `device` object when using a 3-legged access token, the API will validate that the device identifier provided matches the one associated with the access token. + + - If there is a mismatch, the API will respond with a `403 - INVALID_TOKEN_CONTEXT` error, indicating that the device information in the request does not match the token. + + ### Error handling for unidentifiable devices: + + - If the `device` object is not included in the request and the device information cannot be derived from the 3-legged access token, the server will return a 422 `UNIDENTIFIABLE_DEVICE` error. + + ### Restrictions for tokens without an associated authenticated identifier: + + - For scenarios which do not have a single device identifier associated to the token during the authentication flow, e.g. 2-legged access tokens, the `device` object MUST be provided in the API request. This ensures that the device identification is explicit and valid for each API call made with these tokens. + termsOfService: http://swagger.io/terms/ + contact: + email: sp-location-insights@lists.camaraproject.org + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ +servers: + - url: "{apiRoot}/device-visit-location/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: DeviceVisitLocation + description: Operations to retrieve device visit location information. +paths: + /retrieve: + post: + security: + - openId: + - device-visit-location:retrieve + tags: + - DeviceVisitLocation + summary: Retrieves device visit location information + description: Retrieves the latest visit locations of a device within a given + time window. + operationId: retrieveDeviceVisitLocation + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveVisitLocationRequest" + example: + device: + phoneNumber: "+123456789" + startTime: 2024-04-23T14:44:18.165Z + endTime: 2024-04-30T14:44:18.165Z + responses: + "200": + description: Device Visit Location query result + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveVisitLocationResponse" + example: + geoCodeList: + - countryCode: CN + codeType: PostalCode + codeValue: "110000" + - countryCode: CN + codeType: PostalCode + codeValue: "310000" + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/RetrieveVisitLocationBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/RetrieveVisitLocationNotFound404" + "422": + $ref: "#/components/responses/Generic422" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" +components: + securitySchemes: + openId: + type: openIdConnect + description: to support Consent Management + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + schemas: + RetrieveVisitLocationRequest: + type: object + description: Request with a device as identifier,starttime and endtime + required: + - startTime + - endTime + properties: + device: + $ref: "#/components/schemas/Device" + startTime: + type: string + format: date-time + description: Start date time of the time window. If not provided, the default is + the past seven days from the request time. It must follow [RFC + 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and + must have time zone. Recommended format is + yyyy-MM-dd'T'HH:mm:ss.SSSZ. + endTime: + type: string + format: date-time + description: End date time of the time window. If not provided, the default is + the past seven days from the request time. It must follow [RFC + 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and + must have time zone. Recommended format is + yyyy-MM-dd'T'HH:mm:ss.SSSZ. + RetrieveVisitLocationResponse: + type: object + description: Contains the list of geoCode objects representing the visited locations. + required: + - geoCodeList + properties: + geoCodeList: + type: array + items: + $ref: "#/components/schemas/geoCode" + minItems: 1 + geoCode: + type: object + properties: + countryCode: + type: string + description: Code for the country where the location is is located. Following + the `ISO 3166 ALPHA-2` standard, for example, "CN" represents China, + "US" represents the United States, etc. + codeType: + type: string + description: The type of code.This field is used to specify the geographic + encoding type used, with a fixed value of `PostlCode` in the current + version. + codeValue: + type: string + description: The actual value of the code,representing the specific encoding + value of the corresponding codeType. + required: + - countryCode + - codeType + - codeValue + Device: + description: >- + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + + * `ipv6Address` + + * `phoneNumber` + + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + prefixed with '+'. + type: string + pattern: ^\+[1-9][0-9]{4,14}$ + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. + In 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the + telephone number, the network access identifier is not subjected to + portability ruling in force, and is individually managed by each + operator. + type: string + example: 123456789@domain.com + DeviceIpv4Addr: + type: object + description: >- + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: + - publicAddress + - privateAddress + - required: + - publicAddress + - publicPort + example: + publicAddress: 84.125.93.10 + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: 84.125.93.10 + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: The device should be identified by the observed IPv6 address, or by + any single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + ErrorInfo: + type: object + description: Error information + required: + - message + - status + - code + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + responses: + RetrieveVisitLocationBadRequest400: + description: >- + Bad Request. + + In addition to regular scenario of `INVALID_ARGUMENT`, other scenarios may exist: + + - Indicated endTime is earlier than the startTime ("code": "DEVICE_VISIT_LOCATION.INVALID_END_DATE","message": "Indicated endTime is earlier than the startTime.") + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - DEVICE_VISIT_LOCATION.INVALID_END_DATE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_INVALID_END_DATE: + value: + status: 400 + code: DEVICE_VISIT_LOCATION.INVALID_END_DATE + message: Indicated endTime is earlier than the startTime. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required + scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the + API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + RetrieveVisitLocationNotFound404: + description: >- + Not found. + + In addition to regular scenario of `NOT_FOUND`, other scenarios may exist: + + - Device identifier not found ("code": "DEVICE_NOT_FOUND","message": "Device identifier not found."). + + - Unable to find the visit location information of the device within the given time window, it may be due to the device being offline ("code": "DEVICE_VISIT_LOCATION.DATA_NOT_FOUND","message": "Unable to find the visit location information of the device within the given time window"). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + - DEVICE_VISIT_LOCATION.DATA_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + DATA_NOT_FOUND: + description: Unable to find the visit location information of the device within + the given time window + value: + status: 404 + code: DEVICE_VISIT_LOCATION.DATA_NOT_FOUND + message: Unable to find the visit location information of the device within the + given time window. + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 405 + code: + enum: + - METHOD_NOT_ALLOWED + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 406 + code: + enum: + - NOT_ACCEPTABLE + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) + indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by + the client through `Accept-*` headers. + Generic412: + description: Failed precondition + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 412 + code: + enum: + - FAILED_PRECONDITION + examples: + GENERIC_412_FAILED_PRECONDITION: + description: Indication by the API Server that the request cannot be processed + in current system state + value: + status: 412 + code: FAILED_PRECONDITION + message: Request cannot be executed in the current system state. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - IDENTIFIER_MISMATCH + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_IDENTIFIER_MISMATCH: + description: Inconsistency between identifiers not pointing to the same device + value: + status: 422 + code: IDENTIFIER_MISMATCH + message: Provided identifiers are not consistent. + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or + phone number identification cannot be derived from the 3-legged + access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number + has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as + far as possible to get the objective to reach aligned + implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 502 + code: + enum: + - BAD_GATEWAY + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage + the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to + maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 504 + code: + enum: + - TIMEOUT + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. diff --git a/original/DeviceVisitLocation/documentation/API_documentation/README.MD b/original/DeviceVisitLocation/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceVisitLocation/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/DeviceVisitLocation/documentation/SupportingDocuments/README.MD b/original/DeviceVisitLocation/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/DeviceVisitLocation/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/EdgeApplicationManagement/README.md b/original/EdgeApplicationManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8f97063df7b90c2b13f81955764237d8b33508d0 --- /dev/null +++ b/original/EdgeApplicationManagement/README.md @@ -0,0 +1,42 @@ + + + + + + + + + +# EdgeApplicationManagement + +Sandbox API Repository to describe, develop, document, and test the EdgeApplicationManagement Service API(s) within the Sub Project [EdgeCloud](https://lf-camaraproject.atlassian.net/wiki/x/ujLe). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) !! to be updated when wiki page for the repository is created + +## Scope + +* Service API “EdgeApplicationManagement” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * Manage the lifecycle of Edge applications and instances + * Discover an operator's Edge Cloud zones and their status. +* Describe, develop, document, and test the API(s) +* Started: May 2024 (as part of the [Edge Cloud](https://github.com/camaraproject/EdgeCloud) sub project) + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/EdgeApplicationManagement/code/API_definitions/README.MD b/original/EdgeApplicationManagement/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/EdgeApplicationManagement/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/EdgeApplicationManagement/documentation/API_documentation/README.MD b/original/EdgeApplicationManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/EdgeApplicationManagement/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/EdgeApplicationManagement/documentation/SupportingDocuments/README.MD b/original/EdgeApplicationManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/EdgeApplicationManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/EdgeCloud/README.md b/original/EdgeCloud/README.md new file mode 100644 index 0000000000000000000000000000000000000000..84a953f4942a7b4079f4b782ae60fbe4cc96e4b9 --- /dev/null +++ b/original/EdgeCloud/README.md @@ -0,0 +1,52 @@ + + + + + + + + + +# EdgeCloud + +Sandbox API Repository to describe, develop, document, and test Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) +* Warning + +> [!WARNING] +> After the CAMARA Spring25 meta release, the following APIs have been separated into 5 individual repositories: +> - [SimpleEdgeDiscovery](https://github.com/camaraproject/SimpleEdgeDiscovery) +> - [ApplicationEndpointDiscovery](https://github.com/camaraproject/ApplicationEndPointDiscovery) +> - [TrafficInfluence](https://github.com/camaraproject/TrafficInfluence) +> - [ApplicationEndpointRegistration](https://github.com/camaraproject/ApplicationEndpointRegistration) +> - [OptimalEdgeDiscovery](https://github.com/camaraproject/OptimalEdgeDiscovery) +> +> **For these APIs:** This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + +**For the EdgeApplicationManagement API:** API development will continue in this repository until further notice + +## Scope + +* Service APIs for “Edge Cloud” (see APIBacklog.md) +* It provides the customer with the ability to: + * Discover the closest edge cloud zone to a given device (https://github.com/camaraproject/SimpleEdgeDiscovery). + * Provide and manage application images to be deployed on resources within the operator network. + * Use reserved compute resources within the operator network for the deployment of applications on VMs or containers. + * Influence the traffic routing from the user device toward the Edge instance of the Application (https://github.com/camaraproject/TrafficInfluence). + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: 5th July 2022 + +# Release Information + +# Contributing + +* Meetings + * [Registration](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Schedule: Tuesdays 1400-1500 UTC, every two weeks. + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/Edge+Cloud) + +* Mailing list + * Subscribe / unsubscribe to the mailing list of this Sub Project [https://lists.camaraproject.org/g/sp-edc](https://lists.camaraproject.org/g/sp-edc). + * A message to the community of this Sub Project can be sent using [sp-edc@lists.camaraproject.org](sp-edc@lists.camaraproject.org). diff --git a/original/EdgeCloud/code/API_definitions/edge-application-management.yaml b/original/EdgeCloud/code/API_definitions/edge-application-management.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e1cafbbbbe9e560681040d75d4c095a0508e48e5 --- /dev/null +++ b/original/EdgeCloud/code/API_definitions/edge-application-management.yaml @@ -0,0 +1,2041 @@ +--- +openapi: 3.0.3 +info: + title: Edge Application Management API + version: wip + description: | + Edge Application Management API allows API consumers to manage the + Life Cycle of an Application and to Discover Edge Cloud Zones. + # Overview + The reference scenario foresees a distributed Telco Edge Cloud where any + Application Delevoper, known as an Application Provider, can host and + deploy their application according to their specifications and operational + criteria (e.g. within an specific geographical zone for data protection + purposes, ensure a minimum QoS for the application clients, etc). + Through Telco Edge Cloud services Developers around the globe can be + benefit from the traditional Cloud strengths but expertise and advantages + of the Mobile Network Operators offering to their users an evolved + experience for XR, V2X, Holographic and other new services. + + # Introduction + The Edge Application Management API provides capabilities for lifecycle + management of application, instances and edge cloud zone discovery. + Lifecycle Management allows Application Provider to onboard + their application to the Edge Cloud Platform which do bookkeeping, + resource validation and other pre-deployment operations. + Application details can contain components network specification, + package type (QCOW2, OVA, CONTAINER, HELM, CSAR), operating system details and + respository to download the image of the desired application. + Once the application is available on the Edge Cloud + Platform, the Application Provider can instantiate the application. + Edge Cloud Provider helps Application Provider to decide where to + instantiate the applications allowing them to retrieve a list of + Edge Cloud Zones that meets the provided criteria. + + This discovery can be filtered by an specific geographical region + (e.g when data residency is need) and by status (active, inactive, unknown) + Application Provider can ask the Edge Cloud Platform to instantiate the + application to one or several Edge Cloud Zones that meet the criteria. + Typically when more than one Edge Cloud Zone is required in the same + geographic boundary, Application Provider can define instead + the entire Edge Cloud Region. + + Application Provider can retrieve the information of the instances + for a given application, the information could be the Edge Cloud Zone + where the instance is, status (ready, instantiating, failed, + terminating, unknown) and endpoint (ip, port, fqdn). + Application Provider can terminate an instance of an application + (appInstanceId) or all the instances for a given appId. + + # Quick Start + The usage of this API is based on several resources including GSMA + Edge Platform, Public Cloud and SDOs, to define a first approach on the + lifecycle management of application instances and edge cloud zones discovery + + Before starting to use the API, the developer needs to know about + the below specified details. + + __Application Management__ + * __submitApp__ - Submits application details to an Edge Cloud Provider. + Based on the details provided, Edge Cloud Provider shall do bookkeeping, + resource validation and other pre-deployment operations. + * __deleteApp__ - Removes an application from an Edge Cloud Provider, + if there is a running instance of the given application, + the request cannot be done. + * __getApp__ - Retrieves the information of a given application. + + __Application Instance Management__ + * __createAppInstance__ Request the Edge Cloud Provider to instatiate + an instance of an application in a given Edge Cloud Zone, + if this parameter is not set, the Edge Cloud Provider will instantiate + the applications in all the Edge Cloud Zones. + * __getAppInstance__ Retrieves the list with information of the instances + related to a given application. + * __deleteAppInstance__ - Removes a given application instance from an Edge + Cloud Zone. + + __Application Deployment Management__ + * __createAppDeployment__ - Requests the Edge Cloud Provider to create and + maintain application instances to multiple Edge Cloud Zones. + * __getAppDeployments__ - Retrieves a list of deployments for a given + application. + * __deleteAppDeployment__ - Terminates a specific application deployment, + removing all associated instances. + + __Edge Cloud information__ + * __getEdgeCloudZones__ List of the operators Edge Cloud Zones and their + status, ordering the results by location and filtering by status + (active/inactive/unknown) + + # Authentication and Authorization + CAMARA guidelines defines a set of authorization flows which can grant API + clients access to the API functionality, as outlined in the document + [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject\ + /IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access\ + -and-user-consent.md). + Which specific authorization flows are to be used will be determined during + onboarding process, happening between the API Client and the Telco Edge + exposing the API, taking into account the declared purpose for accessing the + API, while also being subject to the prevailing legal framework dictated by + local legislation. + + It is important to remark that in cases where personal user data is + processed by the API, and users can exercise their rights through mechanisms + such as opt-in and/or opt-out, the use of 3-legged access tokens becomes + mandatory. This measure ensures that the API remains in strict compliance + with user privacy preferences and regulatory obligations, upholding the + principles of transparency and user-centric data control. + # API documentation + Two operations have been defined in Edge Application Management API. + + *__Application__* - The Application Provider submit application metadata to + the Edge Cloud Platform. The Edge Cloud Platform generates an appId for that + metadata that will be used to instantiate the application within + the Edge Cloud Zone. + + *__Edge Cloud__* - Retrieves all the Edge Cloud Zones available according to + some defined parameters where an application can be instantiated. + + Definitions of terminologies commonly referred + to throughout the API descriptions. + * __Application Provider__ - The provider of the application that accesses + an Edge Cloud Provider to deploy its application on the Edge Cloud. + An Application Provider may be part of a larger organisation, + like an enterprise, enterprise customer of an Edge Cloud Provider, + or be an independent entity. + * __Application__ - Contains the information about the application to be + instantiated. Descriptor, binary image, charts or any other package + assosiated with the application. The Application Provider request contains + mandatory criteria (e.g. required CPU, memory, storage, bandwidth) defined + in an Application. The Edge Cloud Platform generates a unique ID + for an Application that is ready to be instantiated. + * __Application Instance__ - Is an instance (VM or Container based) running + in an Edge Cloud Zone. The Edge Cloud Platform generates a unique ID + for each instance. + * __Application Deployment__ - A specification that defines the requirements + for the Edge Cloud Provider to create and maintain application instances + across multiple Edge Cloud Zones. The deployment ensures that the + application is instantiated and managed consistently across the specified + zones, meeting the defined requirements. + * __Edge Cloud__ - Cloud-like capabilities located at the network edge + including, from the Application Provider's perspective, access to + elastically allocated compute, data storage and network resources, + this access is provided through the Edge Cloud Platform. + * __Edge Cloud Provider__ - Company name of the provider offering the + Edge Services through the Edge Cloud Platform. + Could be an Operator or a Cloud Provider. + * __Edge Cloud Region__ - An Edge Cloud Region is equivalent + to a Region on a Public Cloud. + The higher construct in the hierarchy exposed to an Application + Provider who wishes to deploy an Application on the Edge Cloud and broadly + represents a geography. An Edge CloudRegion typically contains one or + multiple Edge Cloud Zones. + An Edge Cloud Region exists within an Edge Cloud. + * __Edge Cloud Zone__ - An Edge Cloud Zone is the lowest level of + abstraction exposed to an Application Provider who wants to deploy + an Application on Edge Cloud. + Edge Cloud Zones exists within a Edge Cloud Region. + --- + contact: + email: sp-edc@lists.camaraproject.org + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/EdgeCloud + +servers: + - url: "{apiRoot}/edge-application-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Application + description: Application and Application Instance Lice Cycle Management + - name: Edge Cloud + description: Edge Cloud Zones Availability + +paths: + /apps: + post: + security: + - openId: + - edge-application-management:apps:write + tags: + - Application + summary: Submit application metadata to the Edge Cloud Provider. + description: | + Contains the information about the application to be + instantiated in the Edge Cloud + operationId: submitApp + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + The Application Provider request contains mandatory + criteria (e.g. required CPU, memory, storage, bandwidth) and + optional parameters. + content: + application/json: + schema: + $ref: '#/components/schemas/AppManifest' + required: true + responses: + '201': + description: Application created successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/SubmittedApp' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "App already exists" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:apps:read + tags: + - Application + summary: Retrieve a list of existing Applications + description: | + Get the list of all existing Application definitions from the + Edge Cloud Provider that the user has permission to view. + operationId: getApps + parameters: + - $ref: '#/components/parameters/x-correlator' + responses: + '200': + description: List of existing applications + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppManifest' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /apps/{appId}: + get: + security: + - openId: + - edge-application-management:apps:read + tags: + - Application + summary: Retrieve the information of an Application + description: | + Ask the Edge Cloud Provider the information for a given application + operationId: getApp + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with the + application. + Edge Cloud Provider generates this identifier when the application + is submitted. + in: path + required: true + schema: + $ref: '#/components/schemas/AppId' + responses: + '200': + description: Information of Application + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: object + properties: + appManifest: + $ref: '#/components/schemas/AppManifest' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + delete: + security: + - openId: + - edge-application-management:apps:delete + tags: + - Application + summary: | + Delete an Application from an Edge Cloud Provider + description: Delete all the information and content + related to an Application + operationId: deleteApp + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + in: path + description: | + Identificator of the application to be + deleted provided by the Edge Cloud Provider + once the submission was successful + required: true + schema: + $ref: "#/components/schemas/AppId" + responses: + '202': + description: Request accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '204': + description: App deleted + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "App with a running application instance + cannot be deleted" + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /appinstances: + post: + security: + - openId: + - edge-application-management:instances:write + tags: + - Application + summary: Instantiation of an Application + description: | + Ask the Edge Cloud Platform to instantiate an application to an + Edge Cloud Zone. + operationId: createAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Information about the application and where to deploy it. + content: + application/json: + schema: + type: object + required: + - name + - appId + - edgeCloudZoneId + properties: + name: + $ref: '#/components/schemas/AppInstanceName' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + required: true + responses: + '202': + description: Application instantiation accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Location: + description: Contains the URI of the newly created application. + required: true + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/AppInstanceInfo' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Application already instantiated in the given + Edge Cloud Zone" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:instances:read + tags: + - Application + summary: Retrieve the information of Application Instances for a given App + description: | + Ask the Edge Cloud Provider the information of the instances for a + given application + operationId: getAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with + the application. + Edge Cloud Provider generates this identifier when the + application is submitted. + in: query + required: false + schema: + $ref: '#/components/schemas/AppId' + - name: appInstanceId + description: | + A globally unique identifier associated with a running + instance of an application within an specific Edge Cloud Zone. + Edge Cloud Provider generates this identifier. + in: query + required: false + schema: + $ref: '#/components/schemas/AppInstanceId' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + responses: + '200': + description: | + List of application instances. Returns an empty list if no + instances were found or none match the specified query + parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppInstanceInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /appinstances/{appInstanceId}: + delete: + security: + - openId: + - edge-application-management:instances:delete + tags: + - Application + summary: Terminate an Application Instance + description: | + Terminate a running instance of an application within + an Edge Cloud Zone + operationId: deleteAppInstance + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appInstanceId + in: path + description: | + Identificator of the specific application instance + that will be terminated + required: true + schema: + $ref: "#/components/schemas/AppInstanceId" + responses: + '202': + description: | + Request accepted to be processed. It applies for async + deletion process + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '204': + description: Application Instance Deleted + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /deployments: + post: + security: + - openId: + - edge-application-management:deployments:write + tags: + - Application + summary: Deploy an Application + description: | + Ask the Edge Cloud Platform to instantiate an application to several + Edge Cloud Zones. + operationId: createAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Information about the application and where to deploy it. + content: + application/json: + schema: + type: object + required: + - appDeploymentName + - appId + - edgeCloudZones + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRefs: + type: array + items: + $ref: '#/components/schemas/KubernetesClusterRef' + required: true + responses: + '202': + description: Application deployment accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: object + properties: + appDeploymentId: + $ref: '#/components/schemas/AppDeploymentId' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Deployment already exists" + '500': + $ref: '#/components/responses/500' + '501': + $ref: '#/components/responses/501' + '503': + $ref: '#/components/responses/503' + get: + security: + - openId: + - edge-application-management:deployments:read + tags: + - Application + summary: Retrieve a list of Application Deployment for a given App + description: | + Ask the Edge Cloud Provider the information of the Deployments for a + given application + operationId: getAppDeployments + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appId + description: | + A globally unique identifier associated with + the application. + Edge Cloud Provider generates this identifier when the + application is submitted. + in: query + required: false + schema: + $ref: '#/components/schemas/AppId' + - name: appDeploymentId + description: | + A globally unique identifier associated with a existing deployment + of an application. Edge Cloud Platform generates this identifier when + the deployment request in the Edge Cloud Zone is successful. + in: query + required: false + schema: + $ref: '#/components/schemas/AppDeploymentId' + responses: + '200': + description: | + List of application deployments. Returns an empty list if no + deployments were found or none match the specified query + parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/AppDeploymentInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /deployments/{appDeploymentId}: + delete: + security: + - openId: + - edge-application-management:deployments:delete + tags: + - Application + summary: Terminate an Application Deployment + description: | + Delete a deployment terminating all related instances of an application + operationId: deleteAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appDeploymentId + in: path + description: | + Identificator of the specific application deployment + that will be terminated + required: true + schema: + $ref: "#/components/schemas/AppDeploymentId" + responses: + '202': + description: | + Request accepted to be processed. It applies for async + deletion process + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + patch: + security: + - openId: + - edge-application-management:deployments:update + tags: + - Application + summary: Update an Application Deployment + description: | + Update the configuration or properties of an existing application deployment + using JSON Merge Patch semantics (RFC 7396). Only the fields provided in the + request body will be updated. Fields not included in the request will remain unchanged. + + IMPORTANT: When updating array fields (like edgeCloudZones or kubernetesClusterRefs), + JSON Merge Patch will REPLACE the entire array, not merge or append to it. + + This operation may include changing the deployment name, target Edge Cloud Zones, or other updatable fields. + operationId: updateAppDeployment + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: appDeploymentId + in: path + description: | + Identifier of the specific application deployment to be updated. + required: true + schema: + $ref: "#/components/schemas/AppDeploymentId" + requestBody: + description: | + The fields to update for the application deployment using JSON Merge Patch (RFC 7396). + Only the fields included in the request will be updated; omitted fields remain unchanged. + + NOTE: When updating array fields (edgeCloudZones, kubernetesClusterRefs), the entire array + will be REPLACED, not merged. To modify an array, you must include the complete array + with all desired elements in your request. + required: true + content: + application/merge-patch+json: + schema: + type: object + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + kubernetesClusterRefs: + type: array + items: + $ref: '#/components/schemas/KubernetesClusterRef' + examples: + updateDeploymentName: + summary: Update only the deployment name + description: | + This example shows how to update only the deployment name. + Other fields will remain unchanged. + value: + appDeploymentName: "my_updated_deployment" + updateMultipleFields: + summary: Update multiple fields simultaneously + description: | + This example shows how to update both the deployment name + and Edge Cloud Zones in a single request. Remember that both + array fields will be completely replaced with the new values. + value: + appDeploymentName: "production_deployment" + edgeCloudZones: + - "123e4567-e89b-12d3-a456-426614174000" + - "123e4567-e89b-12d3-a456-426614174001" + kubernetesClusterRefs: + - "642f6105-7015-4af1-a4d1-e1ecb8437abc" + - "642f6105-7015-4af1-a4d1-e1ecb8437def" + arrayReplacementExample: + summary: Example of array replacement behavior + description: | + This example demonstrates how arrays are completely replaced in JSON Merge Patch. + + If the current deployment has: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174001", "123e4567-e89b-12d3-a456-426614174002"] + - kubernetesClusterRefs: ["642f6105-7015-4af1-a4d1-e1ecb8437abc", "642f6105-7015-4af1-a4d1-e1ecb8437def"] + + And the user sends this patch: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174003"] + + The result will be: + - edgeCloudZones: ["123e4567-e89b-12d3-a456-426614174000", "123e4567-e89b-12d3-a456-426614174003"] (completely replaced) + - kubernetesClusterRefs: ["642f6105-7015-4af1-a4d1-e1ecb8437abc", "642f6105-7015-4af1-a4d1-e1ecb8437def"] (unchanged, as it wasn't in the patch) + + To add a single zone while keeping existing ones, ALL zones must be included in the request. + value: + edgeCloudZones: + - "123e4567-e89b-12d3-a456-426614174000" + - "123e4567-e89b-12d3-a456-426614174003" + responses: + '200': + description: Application deployment updated successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/AppDeploymentInfo' + '400': + $ref: '#/components/responses/400' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '410': + $ref: '#/components/responses/410' + '409': + description: Conflict + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 409 + code: CONFLICT + message: "Update conflict" + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + + /clusters: + get: + security: + - openId: + - edge-application-management:clusters:read + tags: + - Cluster + summary: | + Retrieve a list of the available clusters filtered by the optional + query parameters. + description: | + List available cluster information + operationId: getClusters + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Cluster. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + - name: clusterRef + description: | + A globally unique identifier for the Cluster. + in: query + required: false + schema: + $ref: '#/components/schemas/KubernetesClusterRef' + - name: edgeCloudZoneId + description: | + Edge Cloud Zone identifier. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudZoneId' + responses: + '200': + description: | + Successful response, returning the cluster's information. + Returns an empty list if no clusters were found or none match + the specified query parameters. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/ClusterInfo' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' + /edge-cloud-zones: + get: + security: + - openId: + - edge-application-management:edge-cloud-zones:read + tags: + - Edge Cloud + summary: Retrieve a list of the operators Edge Cloud Zones and + their status + description: | + List of the operators Edge Cloud Zones and their + status, ordering the results by location and filtering by + status (active/inactive/unknown) + operationId: getEdgeCloudZones + parameters: + - $ref: '#/components/parameters/x-correlator' + - name: region + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudRegion' + - name: status + description: Human readable status of the Edge Cloud Zone + in: query + required: false + schema: + $ref: '#/components/schemas/EdgeCloudZoneStatus' + responses: + '200': + description: | + Successful response, returning the + Available Edge Cloud Zones. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/EdgeCloudZones' + '401': + $ref: '#/components/responses/401' + '403': + $ref: '#/components/responses/403' + '404': + $ref: '#/components/responses/404' + '500': + $ref: '#/components/responses/500' + '503': + $ref: '#/components/responses/503' +components: + securitySchemes: + openId: + description: OpenID Provider Configuration Information. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: | + Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: | + Correlation id for the different services + required: false + schema: + type: string + format: uuid + + schemas: + AccessEndpoint: + type: object + description: | + Application Endpoint for an especific instance that is + running in an specific Edge Cloud Zone. + required: + - port + anyOf: + - required: + - fqdn + - required: + - ipv4Addresses + - required: + - ipv6Addresses + properties: + port: + $ref: '#/components/schemas/Port' + fqdn: + $ref: '#/components/schemas/Fqdn' + ipv4Addresses: + description: IP version 4 of an application instance + type: array + items: + $ref: '#/components/schemas/Ipv4Addr' + minItems: 1 + ipv6Addresses: + description: IP version 6 of an application instance. + type: array + items: + $ref: '#/components/schemas/Ipv6Addr' + minItems: 1 + + AppId: + type: string + format: uuid + description: | + A globally unique identifier associated with the application. + Edge Cloud Platform generates this identifier when the + Application is submitted. + + AppInstanceId: + type: string + format: uuid + description: | + A globally unique identifier associated with a running + instance of an application. + Edge Cloud Platform generates this identifier when the + instantiation in the Edge Cloud Zone is successful. + + AppDeploymentId: + type: string + format: uuid + description: | + A globally unique identifier associated with a existing deployment + of an application. Edge Cloud Platform generates this identifier when + the deployment request in the Edge Cloud Zone is successful. + + AppDeploymentInfo: + type: object + required: + - appDeploymentName + - appDeploymentId + - appId + - edgeCloudZones + - appInstances + properties: + appDeploymentName: + $ref: '#/components/schemas/AppDeploymentName' + appDeploymentId: + $ref: '#/components/schemas/AppDeploymentId' + appId: + $ref: '#/components/schemas/AppId' + edgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZoneId' + appInstances: + type: array + items: + $ref: '#/components/schemas/AppInstanceId' + + AppInstanceInfo: + description: Information about the application instance. + type: object + required: + - name + - appId + - appInstanceId + - appProvider + - edgeCloudZoneId + properties: + name: + $ref: '#/components/schemas/AppInstanceName' + appId: + $ref: '#/components/schemas/AppId' + appInstanceId: + $ref: '#/components/schemas/AppInstanceId' + appProvider: + $ref: '#/components/schemas/AppProvider' + status: + description: Status of the application instance (default is 'unknown') + type: string + enum: + - ready + - instantiating + - failed + - terminating + - unknown + default: unknown + componentEndpointInfo: + description: | + Information about the IP and Port exposed by the + Edge Cloud Platform. + Application Client shall use these access points to reach this + application instance + type: array + items: + type: object + required: + - interfaceId + - accessPoints + properties: + interfaceId: + type: string + pattern: ^[A-Za-z0-9][A-Za-z0-9_]{6,30}[A-Za-z0-9]$ + description: | + This is the interface Identifier that Application Provider + defines when application is being submitted. + accessPoints: + $ref: '#/components/schemas/AccessEndpoint' + minItems: 1 + kubernetesClusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + + AppInstanceName: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the App instance, scoped to the AppProvider + + AppDeploymentName: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the App Deployment, scoped to the AppProvider + + AppManifest: + description: | + Application information and requirements provided by the + Application Provider + properties: + appId: + $ref: '#/components/schemas/AppId' + name: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{1,63}$ + description: Name of the application. + appProvider: + $ref: '#/components/schemas/AppProvider' + version: + type: string + description: Application version information + packageType: + description: Format of the application image package + type: string + enum: + - QCOW2 + - OVA + - CONTAINER + - HELM + - CSAR + operatingSystem: + $ref: '#/components/schemas/OperatingSystem' + appRepo: + description: | + Repository where Application Provider stores the application image + type: object + required: + - type + - imagePath + properties: + type: + type: string + enum: + - PRIVATEREPO + - PUBLICREPO + description: | + Application repository and image URI information. + PUBLICREPO is used of public urls like github, helm repo etc. + PRIVATEREPO is used for private repo managed by the application + developer. Private repo can be accessed by using the app + developer provided userName and password. Password is + recommended to be the personal access token created by developer + e.g. in Github repo. + imagePath: + $ref: '#/components/schemas/Uri' + userName: + type: string + description: | + Username to acces the Helm chart, docker-compose + file or VM image repository + credentials: + type: string + maxLength: 128 + description: | + Password or personal access token created by + developer to acces the app repository. API users can generate + a personal access token e.g. docker clients to use them as + password. + authType: + type: string + enum: + - DOCKER + - HTTP_BASIC + - HTTP_BEARER + - NONE + description: | + The credentials can also be formatted as a Basic + auth or Bearer auth in HTTP "Authorization" header. + checksum: + type: string + description: | + MD5 checksum for VM and file-based images, sha256 + digest for containers + requiredResources: + $ref: '#/components/schemas/RequiredResources' + componentSpec: + description: | + Information defined in "appRepo" point to the application + descriptor e.g. Helm chart, docker-compose yaml file etc. + The descriptor may contain one or more containers and their + associated meta-data. A component refers to additional details + about these containers to expose the instances of the containers + to external client applications. App provider can define one or + more components (via the associated network port) in componentSpec + corresponding to the containers in helm charts or docker-compose + yaml file as part of app descriptors. + type: array + items: + type: object + required: + - componentName + - networkInterfaces + properties: + componentName: + type: string + description: Component name must be unique with an application + networkInterfaces: + description: | + Each application component exposes some ports + either for external users or for inter component + communication. + Application provider is required to specify which ports are + to be exposed and the type of traffic that will flow through + these ports.The underlying platform may assign a dynamic port + against the "extPort" that the application clients will use + to connect with edge application instance. + type: array + items: + type: object + required: + - interfaceId + - protocol + - port + - visibilityType + properties: + interfaceId: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{3,31}$ + description: | + Each Port and corresponding traffic protocol + exposed by the component is identified by a name. + Application client on user device requires this to + uniquley idenify the interface. + protocol: + type: string + enum: + - TCP + - UDP + - ANY + description: | + Defines the IP transport communication + protocol i.e., TCP, UDP or ANY + port: + type: integer + format: int32 + minimum: 1 + maximum: 65535 + description: | + Port number exposed by the component. + Edge Cloud Provider may generate a dynamic port + towards the component instance which forwards + external traffic to the component port. + visibilityType: + description: | + Defines whether the interface is exposed + to outer world or not i.e., external, or internal. + If this is set to "external", then it is exposed + to external applications otherwise it is exposed + internally to edge application components within + edge cloud. When exposed to external world, + an external dynamic port is assigned for UC traffic + and mapped to the extPort + type: string + enum: + - VISIBILITY_EXTERNAL + - VISIBILITY_INTERNAL + minItems: 1 + required: + - name + - version + - appProvider + - packageType + - appRepo + - requiredResources + - componentSpec + + AppProvider: + type: string + pattern: ^[A-Za-z][A-Za-z0-9_]{7,63}$ + description: Human readable name of the Application Provider. + + ClusterInfo: + description: Kubernetes cluster information + required: + - name + - provider + - clusterRef + - edgeCloudZoneId + properties: + name: + type: string + description: | + Name of the Cluster, scoped to the Provider + provider: + $ref: '#/components/schemas/AppProvider' + clusterRef: + $ref: '#/components/schemas/KubernetesClusterRef' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + version: + type: string + description: Kubernetes version of the cluster. + nodePools: + description: Node Pools in the cluster. + type: array + items: + $ref: '#/components/schemas/KubernetesNodePool' + minItems: 1 + + EdgeCloudProvider: + type: string + description: Human readable name of the Edge Cloud Provider. + + EdgeCloudRegion: + type: string + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + + EdgeCloudZones: + type: array + items: + $ref: '#/components/schemas/EdgeCloudZone' + minItems: 1 + description: | + A collection of Edge Cloud Zones where the Application Provider can + instantiate an Application Instance. + additionalProperties: false + + EdgeCloudZoneId: + type: string + format: uuid + description: | + Unique identifier created by the Edge Cloud Platform to identify an + Edge Cloud Zone within an Edge Cloud. + + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a + combination of the value of the Edge Cloud Zone Id object + and the value of the Edge Cloud Provider + object. This value is used to identify an Edge Cloud zone + between Edge Clouds from different Edge Cloud Providers. + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + properties: + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + edgeCloudZoneName: + $ref: '#/components/schemas/EdgeCloudZoneName' + edgeCloudZoneStatus: + $ref: '#/components/schemas/EdgeCloudZoneStatus' + edgeCloudProvider: + $ref: '#/components/schemas/EdgeCloudProvider' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + minItems: 1 + + EdgeCloudZoneName: + type: string + description: | + Human readable name of the geographical zone of + the Edge Cloud. Defined by the Edge Cloud Provider. + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + ErrorInfo: + type: object + description: Information about the error + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + Fqdn: + type: string + description: | + Full qualified domain name of an application instance + + GpuInfo: + type: object + description: Information about the supported GPUs + required: + - gpuMemory + - numGPU + properties: + gpuMemory: + type: integer + description: GPU memory in mega bytes + numGPU: + type: integer + description: Number of GPUs + + K8sAddons: + description: | + Addons for the Kubernetes cluster. + Additional addons should be defined in application the helm chart + (Service Mesh, Serverless, AI). + type: object + properties: + monitoring: + type: boolean + example: true + default: false + description: Enable monitoring for Kubernetes cluster. + ingress: + type: boolean + example: true + default: false + description: Enable ingress for Kubernetes cluster. + + K8sNetworking: + description: | + Kubernetes networking definition + type: object + properties: + primaryNetwork: + description: Definition of Kubernetes primary Network + type: object + properties: + provider: + description: CNI provider name + type: string + example: cilium + version: + description: CNI provider version + type: string + example: "1.13" + additionalNetworks: + description: Additional Networks for the Kubernetes cluster. + type: array + items: + type: object + description: Additional network interface definition + properties: + name: + description: Additional Network Name + type: string + example: net1 + interfaceType: + description: | + Type of additional Interface: + netdevice: (SR-IOV) A regular kernel network device in the + Network Namespace (netns) of the container + vfio-pci: (SR-IOV) A PCI network interface directly mounted + in the container + interface: Additional interface to be used by cni plugins + such as macvlan, ipvlan + Note: The use of SR-IOV interfaces automatically + configure the required kernel parameters for the nodes. + type: string + example: vfio-pci + enum: + - netdevice + - vfio-pci + - interface + + AdditionalStorage: + description: Additional storage for the application. + type: array + items: + type: object + required: + - storageSize + - mountPoint + properties: + name: + type: string + description: Name of additional storage resource. + example: logs + storageSize: + type: string + description: Additional persistent volume for the application. + example: 80GB + pattern: ^\d+(GB|MB)$ + mountPoint: + type: string + description: Location of additional storage resource. + example: /logs + + Vcpu: + type: string + pattern: ^\d+((\.\d{1,3})|(m))?$ + description: | + Number of vcpus in whole (i.e 1), decimal (i.e 0.500) up to + millivcpu, or millivcpu (i.e 500m) format. + example: "500m" + + KubernetesClusterRef: + description: | + A global unique identifier associated with a Kubernetes cluster + infrastructure. + type: string + format: uuid + example: "642f6105-7015-4af1-a4d1-e1ecb8437abc" + + KubernetesNodePool: + description: | + A Kubernetes node pool is a set of Kubernetes nodes that have the + same configuration (vCPU, memory, networking, OS, etc) on each node. + required: + - name + - numNodes + - nodeResources + - scalable + properties: + name: + description: Human readable name of the Kubernetes Node Pool. + type: string + numNodes: + description: Number of nodes in the Node Pool. + type: integer + scalable: + description: | + Indicates if the node pool can be dynamically scaled up by the + system to accomodate more applications, and dynamically scaled + down by the system when there are unused resources. + type: boolean + example: false + nodeResources: + description: Resource configuration of a node. + type: object + required: + - numCPU + - memory + properties: + numCPU: + description: | + Number of whole vcpus for the node. + type: integer + example: 2 + memory: + description: | + Amount of system memory in mega bytes for the node. + type: integer + example: 4096 + + KubernetesResources: + description: Definition of Kubernetes Cluster Infrastructure. + required: + - infraKind + - applicationResources + - isStandalone + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: kubernetes + enum: + - kubernetes + applicationResources: + description: | + Application resources define the resources pool required + by the application to be executed in a Kubernetes clusters. + type: object + properties: + cpuPool: + required: + - numCPU + - memory + - topology + type: object + description: | + CPU Pool refers to the amount of application' resources + that is executed in nodes with CPU only. That means the part + of application that doesn't require GPU or other kind of + acceleration. + CPU pool is not mandatory when the application is executed + exclusively in a GPU pool. + A CPU pool is composed by CPU and memory. + properties: + numCPU: + description: | + Total number of vcpus in whole (i.e 1) of CPU pool. + type: integer + example: 1 + memory: + description: Total memory in mega bytes of CPU pool. + type: integer + example: 1024 + topology: + type: object + description: | + CPU pool topology defines an application's CPU-based + architecture. + When deploying for high availability or redundancy, it + allows for clustering with a configurable number of nodes + and minimum CPU/memory resource per Kubernetes node + requirements. + required: + - minNumberOfNodes + - minNodeCpu + - minNodeMemory + properties: + minNumberOfNodes: + description: | + Minimum number of worker nodes required by the + application. + type: integer + example: 5 + minNodeCpu: + description: | + Minimum number of vcpus in whole (i.e 1) per cluster + node in CPU pool. + type: integer + example: 2 + minNodeMemory: + description: | + Minimum memory in mega bytes per cluster node in + CPU pool. + type: integer + example: 1024 + gpuPool: + required: + - numCPU + - memory + - gpuMemory + - topology + type: object + description: | + GPU Pool refers to the amount of resources of the application + that is executed in nodes with GPU. + GPU Pool is not mandatory when the application is executed + exclusively in a CPU pool. + A GPU pool is composed by memory, CPU and GPU memory + properties: + numCPU: + description: | + Total Number of vcpus in whole (i.e 1) of GPU pool. + type: integer + example: 1 + memory: + description: Total memory in mega bytes of GPU pool. + type: integer + example: 1024 + gpuMemory: + description: Total GPU memory in giga bytes of GPU pool. + type: integer + example: 16 + topology: + type: object + description: | + GPU pool topology defines an application's GPU-based + architecture. + When deploying for high availability or redundancy, it + allows for clustering with a configurable number of nodes + and minimum CPU/memory/GPU memory resource per Kubernetes + node requirements. + required: + - minNumberOfNodes + - minNodeCpu + - minNodeMemory + - minNodeGpuMemory + properties: + minNumberOfNodes: + description: | + Minimum number of worker nodes with GPU required by + the application. + type: integer + example: 2 + minNodeCpu: + description: | + Minimum number of vcpus in whole (i.e 1) per cluster + node in GPU pool. + type: integer + example: 2 + minNodeMemory: + description: | + Minimum memory in mega bytes per cluster node in + GPU pool. + type: integer + example: 1024 + minNodeGpuMemory: + description: Minimum memory in giga bytes per cluster + node in GPU pool. + type: integer + example: 8 + isStandalone: + description: | + Define if the Kubernetes clusters can be reused by other + applications. + type: boolean + example: false + version: + type: string + description: Minimum Kubernetes Version. + example: "1.29" + additionalStorage: + type: string + description: | + Amount of persistent storage allocated to the Kubernetes PVC. + example: 80GB + pattern: ^\d+(GB|MB)$ + networking: + $ref: '#/components/schemas/K8sNetworking' + addons: + $ref: '#/components/schemas/K8sAddons' + + VmResources: + description: Definition of Virtual Machine Infrastructure + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: virtualMachine + enum: + - virtualMachine + numCPU: + type: integer + description: | + Number of vcpus in whole (i.e 1) + example: 1 + memory: + type: integer + example: 1024 + description: Memory in mega bytes + additionalStorages: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + DockerComposeResources: + description: Definition of Docker Compose Infrastructure + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: dockerCompose + enum: + - dockerCompose + numCPU: + type: integer + description: | + Number of vcpus in whole (i.e 1) + example: 1 + memory: + type: integer + example: 1024 + description: Memory in mega bytes + storage: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + ContainerResources: + description: Container Infrastructure Definition + type: object + required: + - infraKind + - numCPU + - memory + properties: + infraKind: + description: Type of infrastructure for the application. + type: string + example: container + enum: + - container + numCPU: + $ref: '#/components/schemas/Vcpu' + memory: + type: integer + example: 1024 + description: Memory in mega bytes + storage: + $ref: '#/components/schemas/AdditionalStorage' + gpu: + $ref: '#/components/schemas/GpuInfo' + + Ipv4Addr: + type: string + format: ipv4 + example: "192.168.0.1" + description: | + IP of the device. A single IPv4 address may be specified in + dotted-quad form 1.2.3.4. Only this exact IP number will match the flow + control rule. + + Ipv6Addr: + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IP of the device. A single IPv6 address, following IETF 5952 + format, may be specified like 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + OperatingSystem: + description: | + Information about the Operating System of the application image + type: object + required: + - architecture + - family + - version + - license + properties: + architecture: + description: Type of the OS Architecture + type: string + enum: + - x86_64 + - x86 + example: x86_64 + family: + description: Family to which OS belongs + type: string + enum: + - RHEL + - UBUNTU + - COREOS + - WINDOWS + - OTHER + version: + description: Version of the OS + type: string + enum: + - OS_VERSION_UBUNTU_2204_LTS + - OS_VERSION_RHEL_8 + - OS_MS_WINDOWS_2022 + - OTHER + license: + description: License needed to activate the OS + type: string + enum: + - OS_LICENSE_TYPE_FREE + - OS_LICENSE_TYPE_ON_DEMAND + - OTHER + + Port: + type: integer + description: Port to stablish the connection + minimum: 0 + + RequiredResources: + description: | + Fundamental hardware requirements to be provisioned by the + Application Provider. + oneOf: + - $ref: "#/components/schemas/KubernetesResources" + - $ref: "#/components/schemas/VmResources" + - $ref: "#/components/schemas/ContainerResources" + - $ref: "#/components/schemas/DockerComposeResources" + discriminator: + propertyName: infraKind + mapping: + kubernetes: "#/components/schemas/KubernetesResources" + virtualMachine: "#/components/schemas/VmResources" + container: "#/components/schemas/ContainerResources" + dockerCompose: "#/components/schemas/DockerComposeResources" + + SubmittedApp: + description: Information about the submitted app + type: object + properties: + appId: + $ref: '#/components/schemas/AppId' + + Uri: + type: string + example: https://charts.bitnami.com/bitnami/helm/example-chart:0.1.0 + description: | + A Uniform Resource Identifier (URI) as per RFC 3986, + identifies the endpoint within an Edge Cloud Zone where the user + equipment may connect to the selected application instance + + responses: + '400': + description: Bad request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + message: "Schema validation failed at ..." + '401': + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + message: "Authorization failed: ..." + '403': + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 403 + code: PERMISSION_DENIED + message: "Operation not allowed: ..." + '404': + description: Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + message: "Resource does not exist" + '410': + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 410 + code: GONE + message: "The resource has been permanently removed" + '500': + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + message: "Internal server error: ..." + '501': + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 501 + code: NOT_IMPLEMENTED + message: "Service not implemented" + '503': + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" diff --git a/original/EdgeCloud/documentation/API_documentation/README.md b/original/EdgeCloud/documentation/API_documentation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..6e0f8153ac6e7f3ef000a22dfc9fd941d05e75be --- /dev/null +++ b/original/EdgeCloud/documentation/API_documentation/README.md @@ -0,0 +1 @@ +This document should be deleted upon addition of any file in this folder. diff --git a/original/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story.md b/original/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story.md new file mode 100644 index 0000000000000000000000000000000000000000..b3d0ce9f091590f6440ca72909b2f6e5938571e3 --- /dev/null +++ b/original/EdgeCloud/documentation/API_documentation/User_Stories/Edge.Application.Management.User.Story.md @@ -0,0 +1,83 @@ + +Edge Application Management User Story +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)_ +_Roles are referenced from the ITU-T Cloud Refence Architecture._ + +## Summary +"As an Application Developer, I want to determine the Edge Cloud Zone more suitable for my application, being aware of all the options available their status and region of interest. +I want to be able to put my application available in the selected Edge Cloud Zone or Region in a simpler manner providing both artifacts and metadata for instantiating my application succesfully at the same time I want to be able to terminate +running instances of my application on a particular Edge Zone or Region and also to remove information of the whole application itself ". + +This story includes the whole journey from discovering Edge Cloud Zones available to run instances of the application and terminate them : + + +## Actors, Roles, and Scope +| Actor | Role | Scope | +|-------|------|-------| +|Application Provider (AP) |API Consumer | API requester | +|Operator Platform (OP)|Edge Cloud Provider | API Publisher | +|Edge Infrastructure Provider (EIP)|Edge Cloud Provider| + +Note the role of Edge Cloud Provider may be played by either the Operator or a Hyperscaler. + +## Pre-conditions +The AP has a resource usage agreement with the Operator Platform + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Network operators offers a Multi-access Edge Computing platform in a given territory with several levels of abstraction being the Edge Cloud Zone the lowest one. Network operators offers a service through EdgeCloud APIs that permits application providers to deploy instances of an application in one or several Edge Cloud Zones, and to Applications Users the posibility to chose the most appropriate Edge Cloud Zone available at a given moment| M | +|Pre-conditions|The AP has a resource usage agreement with the Operator Platform| M | +|Begins when|The Application Provider (AP) invokes the EdgeCloud API to submit at application with references to obtain all needed data for their instantiation (container images or VM images and manifests describing required resources by an application)| M | +|Step 1|The OP authorizes the request (terminates with a notification to the AP if it is not valid)| M | +|Step 2|The OP validates the request (terminates with a notification to the AP if content is not valid)| M| +|Step 3|The OP stores the app information and returns an Id for reference (terminates with a notification to the AP if error)| M | +|Step 4|The OP request information of currently available Edge Cloud Zones and Regions and their status| M | +|Step 4|The AP invokes the EdgeCloud API to instantiate the application in a given Region, it can also include an specific Edge Cloud Zone referencing previously generated appId | M | +|Step 5|The OP validates the request and if AppId and parameters provided are valid, returns an object including references to one instance Id per Edge Cloud Zone with an instantiation status "instantiating" and starts deploying app instance in EdgeCloud Zones that meet the input criteria| M | +|Step 6|The AP may request updated information of existing app instances of a given app. Possible status for app instantiation includes "ready" also information for endpoint info is provided for the app instance| O | +|Step 7|App instance may provide service for end users | O | +|Step 8|The AP request termination of one app instance (optionally all app instances in a given region) | M | +|Step 8|The OP validates the request (terminates with a notification to the UE if content is not valid e.g. given appId does not exist)| M| +|Step 9|The OP response to the AP and starts the termination of the app instance, moving its status to terminating| M| +|Step 10|The UE connects to the provided EAS and start using the application| M| +|Ends when|The UE connects to the EAS| M | +|Post-conditions|The UE is connected to the most adequate EAS, it may request to reconnect (repeat Step 10) at any time if the perceived quality is not adequate| M | +|Exceptions|
                                                                        • During the step 2 the , the OP can not be able to download the image
                                                                        • During the step 5 the Edge cloud zone resources are not available | M | + + + +## Flow +```mermaid +sequenceDiagram + participant AP + participant OP + participant EIP + Note over AP,OP: PRE App on device attached
                                                                          to operator network + Note over AP,OP: PRE App developer registered,
                                                                          authenticated and authorised + AP->>OP: GET /edge-cloud-zone + OP->>AP: Returns the information about the Edge cloud zones (edgeCloudZoneInfo) + alt app has a local mapping of server endpoints to Edge Cloud Zones + AP->>OP: POST /app Information about app to be instantiate(appManifest) + OP->>AP: Returns the identificator of the submitted app (appId) + AP->>OP: GET /app?appId=UUID Information about app(appId) to be instantiate(appManifest) + OP->>AP: Returns the information requested (appManifest) + AP->>OP: DELETE /app (appId) Delete app for a given appId (Manifest and any related information) + OP->>AP: Request accepted + AP->>OP:POST /app Instantiate application (appId) in a determinated Edge Cloud Zone(edgeCloudZoneId) + OP->>EIP: Instantiate instance in a determinated Edge Cloud Zone(edgeCloudZoneId) + EIP->>OP: Application instantiated + OP->>AP:Returns the appInstance created + AP->>OP: GET /app (appId) /Instance?appID=UUID Information about app(appId) instantiated (appInstanceInfo) + OP->>AP: Returns the application instance information + AP->>OP: DELETE /app (appId) DELETE Running instance for a given appId. + alt delete only the instance related with the appId + OP->>EIP: Delete instance + EIP->>OP: Instance deleted + OP->>AP: Application instance deleted + end + end +``` + + + + diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816.md b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816.md new file mode 100644 index 0000000000000000000000000000000000000000..0a799fbe1f95dd51dc19a571326b6c96f2cd22c9 --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_2020816.md @@ -0,0 +1,36 @@ +# MOM - 2020816 + +**Date:** 16-July-2022 + +## Attendees + +* Andrew Wajs (Scenera) +* Christoph Neumann (Broadpeak) +* Alexandru Ciinaru (Orange) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Landon Cox (MSFT) +* Mark Cornall (GSMA) +* Toshiyasu Wakayama (KDDI) +* Jesse Bijl – (EdgeXR) +* Thomas Vits – (EdgeXR) +* Jon Gainsley – (EdgeXR) +* Mahesh Chapalamadugu – (5GFF) +* Raghuram Parvataneni - (5GFF) +* Syed Rehman – (5GFF) +* Kevin Smith (5GFF) +* Urvika +* David Ferreira Antoniello (TEF) +* Aurelia Martinez Guerra (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| EdgeXR API proposal | EdgeXR | EdgeXR generated 2 API pull requests for thisgroup: *App APIs* [#26](https://github.com/camaraproject/EdgeCloud/pull/26) and *App session and Discovery APIs* [#27](https://github.com/camaraproject/EdgeCloud/pull/27). Jon Gainsley made a general overview of each one. During the session, the possibility of sharing the call flow or sequence diagram of the APIs was requested. EdgeXR will fetch this information and share it. | +| Comment - Pull Request [#21](https://github.com/camaraproject/EdgeCloud/pull/21) | 5GFF | [#21](https://github.com/camaraproject/EdgeCloud/pull/26) - Create EdgeCloudApi\_v0.0.5. yaml: Added a list of API questions today in the pull request. An additional specific session is proposed to discuss the points and questions. It was asked who would be interested in participating, the invitation will be sent to all participants. | +| Comment - Pull Request [#24](https://github.com/camaraproject/EdgeCloud/pull/24) | 5GFF | [#24 - UNI API](https://github.com/camaraproject/EdgeCloud/pull/26): Comments from 5GFF about removing or not the UNI API in this CAMERA group. Mahesh gives first feedback indicating that it will not be very easy for non-Telco users to use the API. This argument is complemented with additional points in the pull request. On the part of Telefonica, it is internally evaluating to have an answer as soon as possible. If necessary, a specific session can be established to discuss this point. Kevin explained that the term 'UNI' is specifically defined in public GSMA materials as requiring a client SDK/middleware ('User Client') on the client UE; and that 5GFF does not require that User Client. 5GFF API allows an application in the UE to call HTTP(S) operator-hosted APIs directly without requiring any additional SDK to be on the UE. | +| Draft Proposal for contributions and approval process in WG - Pull request by DT - [#20](https://github.com/camaraproject/EdgeCloud/pull/26) | DT | It is proposed to work with different subbranches. During the last two weeks, no comments have been received on what was proposed by DT, so it is assumed that all the members of this group agree with this proposal. The next step will be to move the 5GFF contribution to a sub-branch and work on different branches in order to push the proposal to the master branch for approval. In parallel, the way to work to validate the 3 current proposals (MEC Contribution, 5GFF Contribution and EdgeXR Contribution) will be having technical meetings to discuss each point and have the final decision. EdgeXR is interested in managing and organizing these activities. The proposal is that Thomas Vits prepare and elaborate a first proposal for the next technical meeting during the next 2 weeks and have a status in the next bi-weekly session. Different technical activities will be worked on in parallel. | +| Next steps | EdgeXR & TEF | Telefonica and EdgeXR will discuss the next steps to follow will be discussed, beginning with the analysis with the superposition of each proposal and, as a second step, defining the Action Points to have the Edge Cloud API family with all the required functionalities, the discussion of adding or not the UNI API to the Edge Cloud API family | diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719.md b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719.md new file mode 100644 index 0000000000000000000000000000000000000000..951107a4d5839f2f914fa387042639636f2d6a30 --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220719.md @@ -0,0 +1,43 @@ +## APMeting Information + +**Date:** 19-July-2022 + +## Attendees + +* +* Andrew Wajs (Scenera) +* Babu Narayan (Nabstract) +* Christoph Neumann (Broadpeak) +* Alexandru Ciinaru (Orange) +* Tuan Tran (Broadpeak) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Kevin Smith (5GFF) +* Larry Homer  (Intel) +* Landon Cox (MSFT) +* Sylvain Morel (Orange) +* Raffaele Passannanti (TIM) +* Fabrizio Moggio (TIM) +* Tom van Pelt (GSMA) +* Toshiyasu Wakayama (KDDI) +* Yamina Kelm (DT) +* Shilpa Padgaonkar (DT) +* Eric Murray (Vodafone) +* Jesse Bijl +* Thomas Vits +* Aurelia Martinez Guerra (TEF) +* David Ferreira Antoniello (TEF) +* Cristina Santana (TEF) +* José Antonio Ordoñez (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| API Deployment | Capgemini & TEF | TheYAML Swagger associated with the APIs proposed and created by  Orange, DT,Capgemini and Telefonica was presented and detailed. It is the initial ideathat is presented as a starting point to be complemented, edited and reviewedby the participants.  | +| Edge API Family proposal | Capgemini & TEF | An analysis realizedby Telefonica associated with the 5GFF APIs and the Deployment APIs, and thepossible relationship between them, was presented. 
                                                                          https://github.com/camaraproject/EdgeCloud/blob/main/documentation/Presentation/EdgeXR\_forCAMARAEdgeCloudWG\_20220719.pdf | +| EdgeXR Presentation | EdgeXR | Thomas Vitsintroduces EdgeXR and indicates that they want to support and be part of thedevelopment of the CAMARA APIs, taking advantage of the experience gainedduring the MobiledgeX stage. The presentation is included. 
                                                                          https://github.com/camaraproject/EdgeCloud/blob/main/documentation/Presentation/EdgeXR\_forCAMARAEdgeCloudWG\_20220719.pdf | +| | | | +| | | | diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802.md b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802.md new file mode 100644 index 0000000000000000000000000000000000000000..323539add50b44c12ff39c246ffea73761fd5d5e --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220802.md @@ -0,0 +1,41 @@ +## AP Meting Information + +Date: 02 –August - 2022 + +## Attendees + +* Andrew Wajs (Scenera) +* Alexandru Ciinaru (Orange) +* Tuan Tran (Broadpeak) +* Deepak Gunjal (Capgemini) +* Brett Hill (5GFF) +* Larry Homer (Intel) +* Tom van Pelt (GSMA) +* Toshiyasu Wakayama (KDDI) +* Yamina Kelm (DT) +* Shilpa Padgaonkar (DT) +* Thomas Vits (EdgeXR) +* Emil Zhang +* Kevin Xu +* Mahesh Chapalamadugu (5GFF) +* Mark Cornall (GSMA) +* Urvika +* Larry Horner (Intel) +* Vaibhav Mehta (Nabstract) +* Alexandre Harmand (TEF) +* David Ferreira Antoniello (TEF) +* Aurelia Martinez Guerra (TEF + +
                                                                          +
                                                                          +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| #21 API Deployment | Capgemini & TEF | Telefónica in collaboration with Capgemini, uploaded to GitHub as a “pull request” the Edge Deployment API (EdgeCloudApi\_v0.0.5.yaml - [https://github.com/camaraproject/EdgeCloud/pull/21](https://github.com/camaraproject/EdgeCloud/pull/21) 
                                                                          In this YAML it includes the 4 APIs proposed in the first meeting:
                                                                          • Application Artifacts Management
                                                                          • Application Provider Resource Management
                                                                          • Application Onboarding Management
                                                                          • o Application Instance Lifecycle Management
                                                                          Participants can review it and give any additional comments. | +| Edge API Family proposal | EdgeXR | The objective of Telefonica and Capgemini was to have for this meeting a first proposal about the analysis of the parameters to join the 5GFF APIs (Discovery) with the new APIs that were uploaded today (focused on the deployment of the APIs). It was not possible to have it for this week. Two options are proposed:
                                                                          1. Telefonica continues to prepare this new proposal and share it at the next meeting, starting technical activities in parallel to discuss this proposal.
                                                                          2. Another candidate from the group who can collaborate in this analysis in order to have more people involved.
                                                                          Thomas Vits (of EdgeXR) offers to collaborate with this point as another candidate. The objetive is to have a first proposal for the next meeting. | +| #20 Proposal for contributions and approval process in WG              | DT | DT has a "pull request" about the proposal for the Contribution and Approval process of this working group.
                                                                          [https://github.com/camaraproject/EdgeCloud/pull/20](https://github.com/camaraproject/EdgeCloud/pull/20)

                                                                          Shipa Padgaonkar presents the proposal located on the CAMARA GitHub.
                                                                          It is important that everyone review and validate this proposal to make this way of working official.
                                                                          This "pull request" will be maintained until Friday 08/12, if there are no additional comments, it will be validated.
                                                                          It is important that everyone review and validate this proposal to make this way of working official. | +| #25 Draft proposalEdge Cloud GitHub repository Organization | Capgemini & TEF | Deepak,from Capgemini, in conjunction with Telefónica, presented a draft with 3 options for organizing the Edge Cloud GitHub repository. https://github.com/camaraproject/EdgeCloud/pull/25 Initially, during the meeting,some of the participants indicated that option 1 could be the most appropriate.In any case, the presentation is attached and, in case of having additionalcomments, it is established as a deadline to receive them until Friday 08/12. | +| #24 UNI API | Capgemini & TEF | Telefonica& Capgemini open a discussion about the Edge Cloud API Family scope. 
                                                                          This EdgeCloud API Family must include the Edge Discover UNI API, or no? 
                                                                          Telefonicaand Capgemini performed a first analysis of Pro and Cons.
                                                                          Deepakpresented this first analysis. 
                                                                          [https://github.com/camaraproject/EdgeCloud/pull/24](https://github.com/camaraproject/EdgeCloud/pull/24)
                                                                          It isnecessary that the participants can establish if it is important for CAMARA todefine this UNI APIs or must be 3GPP.
                                                                          Theproposal will remain open for the next two weeks, until the next meeting, toestablish a conclusion.. | diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827.md b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827.md new file mode 100644 index 0000000000000000000000000000000000000000..7c90d0ae1566b539a017b53868b42a4f5a6fc7b7 --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_-_20220827.md @@ -0,0 +1,40 @@ +# OM - 20220827 + +Sun, Sep 4, 2022 8:19 AM +
                                                                          +## **Attendees** + +* Andrew Wajs – (Scenera) +* Christoph Neumann – (Broadpeak) +* Tim Epkes - +* Prashant Goswami – +* Deepak Gunjal – (Capgemini) +* Brett Hill – (Telstra - 5GFF) +* Kevin Smith – (Vodafone – 5GFF) +* Landon Cox – (MSFT) +* Mahesh Chapalamadugu - (Verizon – 5GFF) +* Sylvain Morel - (Orange) +* Fabrizio Moggio - (TIM) +* Raffaele Passannanti - (TIM) +* Raghuram Parvataneni - (Telstras – 5GFF) +* Syed Rehman - (Verizon – 5GFF) +* Thomas Vits - (EdgeXR) +* Tom van Pelt - (GSMA) +* Toshiyasu Wakayama (KDDI) +* Urvika +* Alexandre Harmand - (TEF) +* José Antonio Ordoñez - (TEF) +* David +* Ferreira Antoniello - (TEF) +* Aurelia Martínez Guerra - (TEF) + +## Goals + +Go through last MoM action items Identify additional tasks, prepare upcoming ones + +| Item | Who | Description | +| ---- | --- | ----------- | +| CAMRA - Roles | TEF | Markus has defined the differentroles in each CAMARA group in order to be clear about which members will makenew contributions, which members will validate these contributions, etc. This activity has been developed in parallel during these last two weeks and has dedicated part of the time.
                                                                          The toles are:
                                                                          1. **Maintainers: A s**mall group which is acting as Sub Project Managers à listed in the MAINTAINERS.MD of theSub Project
                                                                          2. **Codeowners**: A small group responsible for merging code / documents / PRs à listed in the CODEOWNERS of the SubProject (also technical readable file!)
                                                                          3. Contributors:the whole community for a Sub Project able to contribute à listed as Contributors in GitHub (Markushas to invite, persons have to confirm).
                                                                          | +| Edge Cloud API family | EdgeXR | Analysis of the different contributions to the API (5GFF, OPAG, EdgeX
                                                                          R, New DT contribution). This activity is assigned to a new group in order to analyze all the contributions, define which APIs we must have in this Edge Cloud family, analyze the different APIs to align them with the proposal.
                                                                          In the last session, the EdgeXR team was established as responsible for organizing this small group and starting the activities.
                                                                          Thomas presented the next steps: Have a Kick-off meeting to start working on the activities. A link is attached for those who want to participate and indicate the best option according to availability: ([https://doodle.com/meeting/participate/id/dBLrAQna](https://doodle.com/meeting/participate/id/dBLrAQna)).
                                                                          It is necessary to include in the analyzes of this group the pull request about the questions, doubts and comments of each proposal. For this, it is proposed as the first point on the agenda of the first session to resolve all doubts and questions. | +| ***Comment - Pull Request  #24*** | All | #24 - UNI API: There are different options for this API: Should this API be included in CAMERA? Should 3GPP be used to define this UNI API? Should a part of the API be defined in CAMERA and a part in 3GPP? It is proposed to start a small group to discuss this topic, align and share status in these bi-weekly sessions. It is important to fix this issue, whether or not UNI API is part of the Edge Cloud group, as soon as possible.
                                                                          Deepak (Capgemini) is goin to arrange a short group that is going to have as objetive aligne possiions in this isue | +| Traffic Influence API | TIM | Fabrizio Moggio (TIM) opened a new discussion about the Traffic Influence API. He proposes to work on this API in EdgeCloug grou and that this new API be part og thi Edge Clud API family.

                                                                          It was proposed to Fabrizio in the session that a point be opened in the Backlog group with all the details. This group will decide if it is better to create a new group in CAMARA specifically for Traffic Influence or if this functionality is part of one of the currently available groups. | \ No newline at end of file diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160.md b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160.md new file mode 100644 index 0000000000000000000000000000000000000000..35cb2641a47dd9afe77139c8a36b97477d24742e --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2022/MOM_Convergence_-_202209160.md @@ -0,0 +1,28 @@ +# Meeting Minutes Convergence Substream - 20220916 + +Fri, Sep 16, 2022 17:00 PM +
                                                                          +## **Attendees** + +* Andrew Wajs(Scenera) +* Deepak Gunjal (Capgemini) +* Kevin Smith (Vodafone – 5GFF) +* Mahesh Chapalamadugu (Verizon - 5GFF) +* Syed Rehman (Verizon - 5GFF) +* Thomas Vits (EdgeXR) +* Lev Shvarts (EdgeXR) +* Alexandre Harmand (TEF) +* Rebecca Odenwaelder (Deutsche Telekom) +* Marc Cornall (GSMA) +* Alexandru Ciinaru (Orange) +* Toshiyasu Wakayama (KDDI) + +## Kickoff disucssion + +This call was to initiate the activity of the convergence substream. + +| Item | Who | Description | +| ---- | --- | ----------- | +| Substream Objectives and way of working| All | EdgeXR provided a suggestion on the objectives of this substream, below the aligned outcome after discussion
                                                                          1. Situation: The EdgeCloud Project in CAMARA received already 3 API contributions (from 5GFF, Capgemini, EdgeXR) potentially addressing similar or same functionalities exposing edge cloud services
                                                                          2. Challenge: (Assumption) The goal in CAMARA is to have single API set for a given developer intent (on a specific abstraction layer). <- This was a point of discussion whether that assumption actually holds true or whether different APIs could be feasible for the same intent. No final conclusion taken at this point.
                                                                          3. Solution: Original proposal was to work on the assessment of the current/coming contributions but after discussion we concluded that the initial step to enable this would be to create an aligned taxonomy/terminology. This will ensure that we have the right vocabulary to actually do this assesment acknowledging that background of the distributions is diverse with having different taxonomy in mind.
                                                                      | +| Logistics | All | 1. In order to be able to continue this substream despite of vacations etc. the group agreed to appoint Kevin (VDF/5GFF) as Co-Lead with Thomas (EdgeXR) for this substream.
                                                                      2. Group agreed on a bi-weekly meeting cadence; as we have participants from literally all timezones we agreed to shift timeslots every 2 meetings to the next timzone (e.g. by around 8 hours)
                                                                      3. Agreement that all discussions / documents shall be strictly happen in git| +| Establish aligned Taxonomy| All | As agreed in the initial disucssion the first step is to establish an aligned taxonomy. It was suggested to use the OPG definitions as a basis and then iterate on it in git to come to a consensus. Once good enough (to be agreed by the group when this milestone is hit) the next step (i.e. making an assesment of the scope of the different contributions using that taxonomy) can be initiated. Deepak, Thomas and Mahesh volunteered to get the intitial commit going. | diff --git a/original/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023.md b/original/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023.md new file mode 100644 index 0000000000000000000000000000000000000000..cd25eee02cac810128b444969fdea014d5e4b790 --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/2024/EdgeCloud_MeetingMinuteslinksFromDecember2023.md @@ -0,0 +1,24 @@ +# Edgecloud - Meetings Minutes + +Meeting minutes are kept from December 2023 in https://wiki.camaraproject.org/display/CAM/Edge+Cloud, please refer to that page to follow last updates. + +## December 2023 + +12/12/2024 + +https://wiki.camaraproject.org/display/CAM/2023-12-12%3A+SP-EDC+Minutes + +19/12/2024 + +https://wiki.camaraproject.org/display/CAM/2023-12-19%3A+SP-EDC+Minutes + +## January 2024 + +09/01/2024 + +https://wiki.camaraproject.org/display/CAM/2024-01-09%3A+SP-EDC+Minutes + +23/01/2024 + +https://wiki.camaraproject.org/display/CAM/2024-01-23%3A+SP-EDC+Minutes + diff --git a/original/EdgeCloud/documentation/MeetingMinutes/README.MD b/original/EdgeCloud/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..4b0cb36716f366a96ea3779687188fe6e28747a8 --- /dev/null +++ b/original/EdgeCloud/documentation/MeetingMinutes/README.MD @@ -0,0 +1,5 @@ +# Minutes archive + +From December 2023 the meeting minutes of EdgeCloud calls are within the CAMARA Wiki at [https://wiki.camaraproject.org/display/CAM/Edge+Cloud](https://wiki.camaraproject.org/display/CAM/Edge+Cloud) + +Meeting minutes before December 2023 are here in the repository. diff --git a/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README.md b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..5f66de05e68b7b8ed3d8c3c7095c34e56ac620bd --- /dev/null +++ b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/README.md @@ -0,0 +1,3 @@ +# EdgeCloud – API\_Documentation +
                                                                      +In this folder  will be all the documents about the Edge Cloud API Family \ No newline at end of file diff --git a/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story.md b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..bd8a1431fad031d9e17de1640a0c8afe7de7f5df --- /dev/null +++ b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/User_Stories/EdgeApplicationManagement_User_Story.md @@ -0,0 +1,60 @@ +## Actors, Roles, and Scope +| Actor | Role | Scope | +|-------|------|-------| +|Application Provider (AP) |API Consumer | API Requester | +|Edge Service Provider (ESP)|Edge Cloud Provider|API Publisher | +|MNO|Communications Service Provider|API Publisher | +|User Client(UC)|API Consumer|API Requester | + +Note: the role of Edge Service Provider may be played by different entities, for example: MNOs, Hyperscalers, etc + + + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|Network operators offers a Multi-access Edge Computing platform in a given territory with several levels of abstraction being the Edge Cloud Zone the lowest one. Network operators offers a service through EdgeCloud APIs that permits application providers to deploy instances of an application in one or several Edge Cloud Zones, and to Applications Users the posibility to chose the most appropriate Edge Cloud Zone available at a given moment| M | +|Pre-conditions|The AP has a resource usage agreement with the Operator Platform| M | +|Begins when|The Application Provider (AP) invokes the Edge Application Management API to submit an application with references to obtain all needed data for their instantiation (container images or VM images and manifests describing required resources by an application)| M | +|Step 1|The ESP stores the app information and returns an Id for reference (terminates with a notification to the AP if error)| M | +|Step 2|The Application Provider (AP) request information of currently available Edge Cloud Zones and their status | M| +|Step 3|The MNO provides the availables Edge Cloud Zones where the AP could instantiate the Application| M | +|Step 4|The AP instantiates the application in one Edge Cloud Zone or in Severals| M| +|Step 5|The ESP response to the AP appInstance created| M | +|Step 6|The AP may request updated information of existing app instances of a given app. Possible status for app instantiation includes "ready" also information for endpoint info is provided for the app instance| O | +|Step 7|App instance may provide service for end users | O | +|Step 8|The AP request termination of one app instance (optionally all app instances in a given region) | M | +|Step 9|The ESP validates the request (terminates with a notification to the UE if content is not valid e.g. given appId does not exist)| M| +|Step 10|The ESP responds to the AP and starts the termination of the app instance, moving its status to terminating| M| +|Ends when|The UC connects to the EAS| M | + + + + +## Flow +```mermaid +sequenceDiagram + participant AP + participant MNO + participant ESP(Operator/Hyperscaler) + + Note over AP,MNO: PRE App on device attached
                                                                      to operator network + Note over AP,MNO: PRE App developer registered,
                                                                      authenticated and authorised + Note over MNO,MNO: Edge Application Management API + AP->>ESP(Operator/Hyperscaler): POST/ AP Invokes Edge Application Management API to submit an application with references to obtain all needed data for their instantiation(appManifest) + ESP(Operator/Hyperscaler)->>AP: The Operator stores the app information and returns an Id for reference(appId) + alt app has a local mapping of server endpoints to Edge Cloud Zones + AP->>MNO: GET/edge-cloud-zones AP request information about available Edge cloud zones + MNO->>AP: Returns the name of the available Edge cloud zones for the Application + AP->>ESP(Operator/Hyperscaler):POST/ The AP request to instantiate the App in one or several Edge Clod Zones(Deployment). + ESP(Operator/Hyperscaler)->>AP:Returns the appInstance created + AP->>MNO: GET /app (appId) Information about app(appId) instantiated + MNO->>AP: Returns the application instance information + AP->>MNO: DELETE /app (appId) DELETE Running instance for a given appId. + alt delete only the instance related with the appId + MNO->>ESP(Operator/Hyperscaler): Delete instance + ESP(Operator/Hyperscaler)->>MNO: Instance deleted + MNO->>AP: Application instance deleted + end + end +``` + diff --git a/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta.json b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta.json new file mode 100644 index 0000000000000000000000000000000000000000..764820be8ef4d58c3a8b2af0a29d1ca64e838ad1 --- /dev/null +++ b/original/EdgeCloud/documentation/SupportingDocuments/API_Documentation/unotes/unotes_meta.json @@ -0,0 +1,8 @@ +{ + "name": "", + "isOrdered": true, + "folders": {}, + "files": { + "README": 0 + } +} \ No newline at end of file diff --git a/original/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation.md b/original/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation.md new file mode 100644 index 0000000000000000000000000000000000000000..7145de5aa55ad87d6f205ea41afd9c52eebf242d --- /dev/null +++ b/original/EdgeCloud/documentation/SupportingDocuments/EdgeCloud-Intents-and-API-Mapping-Harmonisation.md @@ -0,0 +1,183 @@ +# Edge Cloud Intents and API Mapping – Harmonisation Document + +_This document is based on the [CAMARA Commonalities template for User Stories](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) and references ITU-T Cloud Reference Architecture roles._ + +--- + +## 1. Summary + +This document provides a harmonised view of **EdgeCloud Intents** and their corresponding **CAMARA APIs**, consolidating the functional flow across discovery, deployment, runtime, and termination stages of the **Edge Cloud lifecycle**. + +The purpose is to bridge earlier MEC & Deployment API proposals with the current **CAMARA Edge Cloud family of APIs**, ensuring a unified lifecycle from **Zone discovery** to **Application endpoint registration and discovery**. + +--- + +## 2. Objectives + +- To define the **intents** supporting the lifecycle of Edge-hosted applications. +- To map these intents to existing and emerging **CAMARA APIs**. +- To support interoperability between **Operator Platforms** and **Application Providers**. +- To prepare the foundation for future harmonisation across **Edge, Application Management, and Network APIs** (e.g., Traffic Influence). + +--- + +## 3. Roles, Actors, and Scope + +| Actor | Role | Scope | +|-------|------|-------| +| Application Provider (AP) | API Consumer | API requester, deploys applications and manages instances. | +| Operator Platform (OP) | Edge Cloud Provider | API publisher, orchestrates resources and exposes APIs. | +| Edge Infrastructure Provider (EIP) | Edge Cloud Provider | Hosts and manages the physical/virtual infrastructure. | +| End User (UE) | Service Consumer | Interacts with applications hosted at the edge. | + +> Note: Edge Cloud Provider may be the Operator or a Hyperscaler. + +--- + +## 4. EdgeCloud Lifecycle Intents Overview + +| **Intent ID** | **Intent Name** | **Purpose / Description** | **Mapped CAMARA API / Status** | +|---------------|----------------|----------------------------|--------------------------------| +| **Intent 1** | Discover EdgeCloud Zones | Discover the closest Edge Cloud Zone to a user device based purely on network topology (shortest network path). | `Simple Edge Discovery API` | +| **Intent 2** | List Available Regions / Capabilities | Discover the best Edge Cloud Zone for an application, considering compute, storage, and network performance requirements beyond distance. | Planned extension of Optimal Edge Discovery | +| **Intent 3** | Retrieve Zone Information | Obtain metadata, KPIs, and current resource availability of a specific Edge Cloud Zone. | `Simple Edge Discovery API` | +| **Intent 4** | Filter / Select Preferred Zones | Apply filters (latency, region) for optimal zone selection. | Planned enhancement within Optimal Edge Discovery | +| **Intent 5** | Register / Onboard Application | Upload manifests, metadata, and container images. | `Edge Cloud Lifecycle Management API` | +| **Intent 6** | Validate Application Metadata | Validate manifests and dependencies before deployment. | Partially covered by Lifecycle Management | +| **Intent 7** | Instantiate Application | Deploy application instances in selected Edge Zones. | `Edge Cloud Lifecycle Management API` | +| **Intent 8** | Scale Application Instance | Adjust resources dynamically (horizontal/vertical). | Future – EdgeCloud Scaling API (proposed) | +| **Intent 9** | Register Application Endpoints | Register deployed app endpoints (URLs, ports, zones). | `Application Endpoint Registration API` | +| **Intent 10** | Update Endpoint Metadata | Modify endpoint details (status, performance). | Within `Application Endpoint Registration API` | +| **Intent 11** | Discover Optimal Application Endpoints | Find best endpoint for a device based on latency or policy. | `Application Endpoint Discovery API` | +| **Intent 12** | Client-Side Endpoint Selection | Allow clients to select among multiple available endpoints. | Optional behaviour of Endpoint Discovery | +| **Intent 13** | Influence Network Traffic | Apply routing rules for premium users or optimisation. | `Traffic Influence API` | +| **Intent 14** | Configure Network Policies | Manage slicing/routing preferences for traffic flows. | Evolution of Traffic Influence | +| **Intent 15** | Monitor Application Performance | Retrieve runtime telemetry: latency, usage, etc. | SessionInsights API | +| **Intent 16** | Retrieve Edge Metrics / Zone Health | Query Edge Zone health and operational metrics. | Under discussion – EdgeCloud Monitoring API | +| **Intent 17** | Automate Policy or Scaling Actions | Enable closed-loop orchestration and scaling triggers. | Future – Edge Orchestration Intent API | +| **Intent 18** | Terminate Application | Decommission instances and release resources. | `Edge Cloud Lifecycle Management API` | +| **Intent 19** | Deregister Application Endpoints | Remove obsolete endpoints from registry. | `Application Endpoint Registration API` | +| **Intent 20** | Audit and Logging | Track API operations, logs, and service usage. | Commonalities Cross-API Logging proposal | +| **Intent 21** | Federated Edge Discovery | Discover edge zones from partner operators/hyperscalers. | Proposed – Edge Federation Discovery API | +| **Intent 22** | Cross-Operator Application Placement | Deploy app instances across federated networks. | Future CAMARA/GSMA initiative | +| **Intent 23** | Consent and Policy Management | Manage end-user consent during discovery/exposure. | Privacy & Consent WG | +| **Intent 24** | Service Quality Enforcement | Apply QoS constraints dynamically per application. | Future – Edge QoS Policy API | +| **Intent 25** | Edge Resource Reservation / Pre-Booking | Reserve compute/storage/network capacity pre-deployment. | Proposed – Edge Reservation API | + +--- + + +## 5. Harmonised EdgeCloud Lifecycle Flow + +```mermaid +flowchart LR + A[Intent 1: Discover Edge Zones] --> B[Intent 3: Retrieve Zone Info] + B --> C[Intent 5: Register Application] + C --> D[Intent 7: Instantiate Application] + D --> E[Intent 9: Register Application Endpoints] + E --> F[Intent 11: Discover Optimal Endpoints] + F --> G[Intent 13: Apply Traffic Influence - optional] + G --> H[Intent 18: Terminate Application] +``` +```mermaid +sequenceDiagram + participant AP as Application Provider + participant OP as Operator Platform + participant EIP as Edge Infrastructure Provider + participant UE as User Equipment + participant AF as Application Function + + Note over AP,OP: Phase 1 - Discovery + AP->>OP: POST /discover-optimal-edge-zones + OP-->>AP: EdgeCloudZone list ordered by proximity + + Note over AP,OP: Phase 2 - Provisioning & Deployment + AP->>OP: POST /applications (Onboard Application) + OP-->>AP: Returns appId + AP->>OP: POST /applications/{appId}/instances + OP->>EIP: Instantiate app in target Edge Zone + EIP-->>OP: Instance ready + OP-->>AP: appInstanceId + status "RUNNING" + + Note over AP,OP: Phase 3 - Endpoint Management + AP->>OP: POST /register (Application Endpoint) + OP-->>AP: endpointId confirmation + + Note over UE,OP: Phase 4 - Runtime & Discovery + UE->>OP: POST /retrieve-optimal-app-endpoints {appId, device} + OP-->>UE: Returns optimal endpoint (EdgeCloudZoneId, endpointURL) + + Note over AF,OP: Phase 5 - Network Optimisation + AF->>OP: POST /traffic-influence (toward EAS) + OP-->>AF: Returns routing configuration ID + UE->>EIP: Connect to optimal EAS endpoint +``` +# CAMARA EdgeCloud Harmonisation Analysis + +## 7. Harmonisation Analysis + +### 7.1 API Relationship Summary + +- **Simple Edge Discovery**: Provides baseline nearest-zone discovery using network proximity. +- **Optimal Edge Discovery**: Extends discovery with richer metadata (zone characteristics, latency, region). +- **Edge Application Management**: Enables deployment and lifecycle control of applications in these zones. +- **Application Endpoint Registration**: Establishes registry of deployed endpoints. +- **Application Endpoint Discovery**: Allows clients or servers to dynamically retrieve optimal endpoints. +- **Traffic Influence**: Complements discovery and lifecycle by providing routing enforcement at the network level. + +### 7.2 Common Design Principles + +- **Entity Alignment**: Shared objects (e.g., `edgeCloudZoneId`, `appId`, `endpointId`) across all APIs. +- **Security Consistency**: All APIs assume OAuth2-based access with clear roles. +- **Consent Integration**: Optional per API (explicit in Discovery and Endpoint APIs). +- **Operator Neutrality**: APIs work across multiple operators via federated exposure models. + +**Conclusion**: CAMARA EdgeCloud APIs collectively address all intents from earlier MEC proposals, forming a continuous lifecycle from discovery → provisioning → runtime → termination. + +## 8. Harmonised Data Model Overview + +| Entity | Description | Referenced In | +|--------|-------------|---------------| +| `edgeCloudZoneId` | Identifier of Edge Cloud Zone | Discovery, Lifecycle, Endpoint APIs | +| `appId` | Unique application identifier | Lifecycle, Endpoint Discovery | +| `appInstanceId` | Deployed instance ID | Lifecycle API | +| `endpointId` | Registered endpoint for a deployed instance | Endpoint Registration & Discovery | +| `deviceId` | Device identifier or token | Discovery and Endpoint Discovery APIs | +| `trafficInfluenceId` | Identifier for a network routing session | Traffic Influence API | + +## 9. Inter-API Dependencies + +| API | Depends On | Dependency Description | +|-----|------------|------------------------| +| Simple Edge Discovery | None | Can be used standalone for planning | +| Optimal Edge Discovery | None | Can be used standalone for planning | +| Edge Application Management | Optimal Edge Discovery | Uses discovered zones for deployment decisions | +| Application Endpoint Registration | Edge Cloud Lifecycle Management | Registers endpoints of instantiated applications | +| Application Endpoint Discovery | Endpoint Registration | Discovers registered endpoints | +| Traffic Influence | Endpoint Discovery | Optimises routing to discovered endpoints | + +**Harmonised APIs together enable a complete closed loop**: +Discovery → Deployment → Registration → Discovery (endpoint) → Influence → Termination. + +## 10. Open Harmonisation Topics + +| Area | Description | Next Step | +|------|-------------|-----------| +| Unified Discovery Schema | Align Simple and Optimal Edge Discovery response objects | Define a shared `EdgeCloudZoneInfo` schema | +| Cross-API Security Scopes | Establish unified OAuth2 roles and scopes | Coordinate with Commonalities WG | +| Consent Management | Define consistent consent-handling process across Discovery and Endpoint APIs | Align with Privacy & Consent WG | +| Federated Operations | Support discovery and lifecycle across multi-operator environments | Introduce Edge Federation API concept | +| Traffic Policy Automation | Enable dynamic network steering based on real-time metrics | Collaborate with Network API group | + +## 11. References + +- **CAMARA – Simple Edge Discovery API**: [User Story](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/main/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md) +- **CAMARA – Optimal Edge Discovery API**: [User Story](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/main/documentation/API_documentation/optimal-edge-discovery-User-Story.md) +- **CAMARA – Edge Application Management**: [User Story](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/API_Documentation/User%20Stories/Edge.Cloud.Lifecycle.Management.User.Story.md) +- **CAMARA – Application Endpoint Registration API**: [User Story](https://github.com/camaraproject/ApplicationEndpointRegistration/blob/main/documentation/API_documentation/application-endpoint-registration-User-Story.md) +- **CAMARA – Application Endpoint Discovery API**: [User Story](https://github.com/camaraproject/ApplicationEndpointDiscovery/blob/main/documentation/SupportingDocuments/API_Documentation/User%20Stories/Application%20Endpoint%20Discovery%20User%20Story.md) +- **CAMARA – Traffic Influence API**: [User Story](https://github.com/camaraproject/TrafficInfluence/blob/main/documentation/API_documentation/traffic-influence-user-story-use-case-1.md) +- **GSMA – Open Gateway & CAMARA Harmonisation Framework**: [Reference](https://www.hcltech.com/sites/default/files/documents/resources/whitepaper/files/2024/09/16/gsma-open-gateway.pdf?utm_source=chatgpt.com) + + + diff --git a/original/EdgeCloud/documentation/SupportingDocuments/README.MD b/original/EdgeCloud/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/EdgeCloud/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/EnergyFootprintNotification/README.md b/original/EnergyFootprintNotification/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8a7ccff6dab931f82341e96600e2878b62c53d26 --- /dev/null +++ b/original/EnergyFootprintNotification/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# EnergyFootprintNotification + +Sandbox API Repository to describe, develop, document, and test the EnergyFootprintNotification Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/aoDJAw) +* [Provider Implementation](https://github.com/camaraproject/EnergyFootprintNotification_PI) + +## Scope + +* Service API(s) “EnergyFootprintNotification” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API(s) provide(s) the customer with the ability to: + * Retrieve the information about the E2E energy consumption and Carbon Footprint for a specified service that is provided by a certain number of active instances of an application. The applications that are monitored for their energy consumption are the ones managed by the operator and that run on top of the operator’s infrastructure. For example the application managed with the [CAMARA Edge Cloud APIs](https://github.com/camaraproject/EdgeCloud). +* Describe, develop, document, and test the API(s) +* Started: January 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/EnergyFootprintNotification/releases/tag/r1.3) (Fall25), with the following API versions: + * **energy-footprint-notification v0.1.0** + [[YAML]](https://github.com/camaraproject/EnergyFootprintNotification/blob/r1.3/code/API_definitions/energy-footprint-notification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/EnergyFootprintNotification/r1.3/code/API_definitions/energy-footprint-notification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/EnergyFootprintNotification/r1.3/code/API_definitions/energy-footprint-notification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/EnergyFootprintNotification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/EnergyFootprintNotification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/EnergyFootprintNotification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly, Tuesday 13:00 – 14:00 UCT + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99704469014?password=31affe33-8c78-42f3-9cec-32efee113700) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/67076164) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list https://lists.camaraproject.org/g/sp-efn. + * A message to the community of this Sub Project can be sent using sp-efn@lists.camaraproject.org. diff --git a/original/EnergyFootprintNotification/code/API_definitions/README.MD b/original/EnergyFootprintNotification/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/EnergyFootprintNotification/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification.yaml b/original/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fa09124c2427d458e1b7ef6b6c2e32b348adc667 --- /dev/null +++ b/original/EnergyFootprintNotification/code/API_definitions/energy-footprint-notification.yaml @@ -0,0 +1,1039 @@ +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Energy Footprint Notification + description: | + ## Overview + The Energy Footprint Notification API provides the API Consumer + with information about the energy consumption and carbon footprint of a + service exposed by a set of applications instances. + ## Introduction + The scenario foresees a service provided by many applications, the Energy + Footprint API provides the API Consumer (e.g. the Service Provider) + with the information about the energy consumption and carbon + footprint (greenhouse gases emissions) of the service produced by the + active applications instances hosted by the Telco Operator. + Note: This API is expected to be used in conjunction with, for example, + the CAMARA Edge Cloud APIs. + + **Example use case and flow:** + + [**Edge Service energy report**](https://github.com/camaraproject/EnergyFootprintNotification/blob/r1.3/documentation/API_documentation/EFN_UserStory_UseCase_1.md) + + ## API Documentation + ## Details + The Energy Footprint Notification API provides, to the API Consumer, + information about the energy consumption and carbon footprint for a + specified service that is provided by a certain number of active instances + of some applications. The API provides information about the aggregated + energy consumption and carbon footprint considering all the active instances + and network involvement, in a specific time period in which the service is + provided to end users. The application instances that are monitored + for their energy consumption are the one managed by the Operator and that + run on top of the Operator’s infrastructure. The service is deployed and + managed via the Operator Platform (e.g via the [CAMARA Edge Cloud APIs](htt\ + ps://github.com/camaraproject/EdgeCloud)). Consequently, the Operator + Platform is aware of all the active instances supporting the service and it + is also aware of the energy consumption in the Data Centers hosting the + applications instances providing the service. The Operator's Network is + deeply involved in the service provisioning, so its energy consumption is + relevant to have and view. The Energy Footprint Notification API also considers the energy + consumption and the carbon footprint for the network traffic generated by + the Operator's subscribers consuming the service. The Service Provider + activates a service using the Operator Platform to instantiate and activate + the application supporting the service in different Edge Data Centers. + The Service Provider onboards the applications, deploys and activates some + instances to enable the service. Service customers use their devices to + access the service. The use of the service produces an energy + consumption alongside the Operator's Network and on the Data Centers hosting + the applications instances. The Energy Footprint Notification API is used by a Service Provider to be + aware of the energy consumption of the service. The Service Provider, + via an Energy Footprint Notification API Consumer, invokes the Energy Footprint Notification API with the identifiers of the + application instances supporting the target service. A period of + time can be specified; it must start after the API subscription and can be limited. + The Energy Footprint Notification API provides back the energy consumption by + the service in that period of time. The Energy Footprint Notification API also provides back the + carbon footprint related to the running of the service. + The Energy Footprint Notification API is an intent based API. + + The Energy Footprint Notification API supports the following Intents: + - Intent1: Which is the overall energy consumption for my service in this + period of time? + - Intent2: Which is the overall carbon footprint for my service in this + period of time? + + The input for the above intents is: + - Input_Intent1: Set of applications identifiers and period of time. + - Input_Intent2: Set of applications identifiers and period of time. + + The output for the above intents is: + - Output_Intent1: energy consumption in Kw/h. + - Output_Intent2: greenhouse gases emission in tonnes. + + The related endpoints are: + - Intent1: /calculate-energy-consumption + - Intent2: /calculate-carbon-footprint + + **The main elements of the Energy Footprint Notification API are:** + + **ReportCreationRequest:** + Information about the target service (as a + set of applications) and the period of time of interest. + The period must start after the API subscription and can be limited. + It includes the parameter "service" which is an array of application + identifiers. The application identifiers are provided by the CAMARA API + used to deploy the applications (e.g. the Edge Application Management API). + + **EnergyResponse:** + Provides to the API Consumer the requested information about the energy + consumption for the target service, considering all the active instances, + in the period of time of interest. + + **CarbonFootprintResponse:** + Provides to the API Consumer the information about the carbon footprint for + the target service, considering all the active instances, in the period of + time of interest. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/EnergyFootprintNotification +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/energy-footprint-notification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. + `api.example.com` or `api.example.com/somepath` +security: + - notificationsBearerAuth: [] +############################################################################ +# Tags # +############################################################################ +tags: + - name: Energy consumption information retrieval + description: Request information on the energy consumption of the service. + - name: Carbon footprint information retrieval + description: Request information on the carbon footprint for the service. +############################################################################ +# Paths # +############################################################################ +paths: + /calculate-energy-consumption: + post: + tags: + - Energy consumption information retrieval + summary: Provides the overall Energy Consumption for the target + Application instances in a certain period of time. + description: Receives as input an object containing the intents from the + API Consumer and provides back the energy consumption with a callback. + operationId: calculateEnergyConsumption + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'energy-footprint-notification:calculate-energy-consumption' + requestBody: + description: Defines the application that provides the service and the + time period under analysis. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + responses: + "201": + description: The request has been acquired. The request identifier is + returned. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created resource + schema: + type: string + description: Link to the created resource + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + callbacks: + onEnergyConsumption: + $ref: "#/components/callbacks/onEnergyConsumptionCalculation" + /calculate-carbon-footprint: + post: + tags: + - Carbon footprint information retrieval + summary: Retrieves the overall carbon footprint for the target Application + instances in a certain period of time. + description: Receives as input an object containing the intents from the + API Consumer and provides back the carbon footprint with a callback. + operationId: calculateCarbonFootprint + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'energy-footprint-notification:calculate-carbon-footprint' + requestBody: + description: Defines the application that provides the service and the + time period under analysis. + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + responses: + '201': + description: The request has been acquired. The request identifier is + returned. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created resource + schema: + type: string + description: Link to the created resource + content: + application/json: + schema: + $ref: '#/components/schemas/ReportCreationRequest' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + callbacks: + onCarbonFootprintCalculation: + $ref: "#/components/callbacks/onCarbonFootprintCalculation" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onEnergyConsumptionCalculation: + # when data is sent, it will be sent to the callback url provided + "{$request.body.subscriptionRequest.sink}": + post: + summary: Provides back the result of the analysis on the energy + consumption + description: once the system has calculated the energy consumption of + the service, this information is provided back to the API Consumer + operationId: energyConsumptionNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the calculated energy consumption + required: true + content: + application/cloudevents+json: + schema: + allOf: + - $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.energy-footprint-notification.v1.energy" + specversion: "1.0" + datacontenttype: "application/json" + data: + requestId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + energyConsumption: 12.87 + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + onCarbonFootprintCalculation: + # when data is sent, it will be sent to the callback url provided + '{$request.body.subscriptionRequest.sink}': + post: + summary: Provides back the result of the analysis on the carbon + footprint + description: once the system has calculated the carbon footprint of + the service, this information is provided back to the API Consumer + operationId: carbonFootprintNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the calculated energy consumption + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.energy-footprint-notification.v1.carbon-footprint" + specversion: "1.0" + datacontenttype: "application/json" + data: + requestId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + carbonFootprint: 45.568 + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + ############################################################################ + # Resources # + ############################################################################ + schemas: + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 2 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.energy-footprint-notification.v1.energy + - org.camaraproject.energy-footprint-notification.v1.carbon-footprint + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.energy-footprint-notification.v1.energy + - org.camaraproject.energy-footprint-notification.v1.carbon-footprint + ReportCreationRequest: + description: resource containing the service under analysis and the + callback information for the API Consumer to be notified with the + results of the analysis. If no "timePeriod" is provided the analysis + is performed from the activation of the first instance of the + Application. + type: object + properties: + service: + type: array + description: list of Application Instance Identifiers. This are the + instances of the applications producing the service under analysis. + items: + $ref: '#/components/schemas/AppInstanceId' + timePeriod: + $ref: "#/components/schemas/TimePeriod" + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + requestId: + type: string + description: Identifier for the request. This + parameter is returned by the API and must be used to update it. + readOnly: true + required: + - service + - subscriptionRequest + AppInstanceId: + type: string + format: uuid + description: | + A globally unique identifier associated with a running + instance of an application. + Edge Cloud Platform generates this identifier when the + instantiation in the Edge Cloud Zone is successful + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required in + CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + required: + - startDate + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.energy-footprint-notification.v1.energy: "#/components/schemas/CloudEventEnergy" + org.camaraproject.energy-footprint-notification.v1.energy.error: "#/components/schemas/CloudEventError" + org.camaraproject.energy-footprint-notification.v1.carbon-footprint: "#/components/schemas/CloudEventCarbonFootprint" + org.camaraproject.energy-footprint-notification.v1.carbon-footprint.error: "#/components/schemas/CloudEventError" + CloudEventEnergy: + description: provides back the energy consumption for the service. The + result of the analysis is a floating point number. The unit of measure + is Kw/h. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + type: object + description: Event details payload + properties: + requestId: + type: string + description: Identifier for the request. This + parameter correlates this response with the request. + readOnly: false + energyConsumption: + type: number + format: float + example: 12.345 + description: the energy consumption for all the instances of the + service. The API is asynchronous, for this reason the value will be + returned back via a callback + CloudEventCarbonFootprint: + description: provides back the carbon footprint of the service. The result + of the analysis is a floating point number. The unit of measure is + tonnes. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + type: object + description: Event details payload + properties: + requestId: + type: string + description: Identifier for the request. This + parameter correlates this response with the request. + readOnly: false + carbonFootprint: + type: number + format: float + example: 45.568 + description: the carbon footprint for all the instances of the + service. The API is asynchronous, for this reason the value will be + returned back via a callback + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Responses # + ############################################################################ + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. Access token does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ENERGY_FOOTPRINT_NOTIFICATION.UNKNOWN_APPLICATION_IDENTIFIER + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Application Identifier unknown + value: + status: 404 + code: ENERGY_FOOTPRINT_NOTIFICATION.UNKNOWN_APPLICATION_IDENTIFIER + message: The target application is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - ENERGY_FOOTPRINT_NOTIFICATION.TIME_PERIOD_OUT_OF_RANGE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_TIME_PERIOD_OUT_OF_RANGE: + description: The parameter "timePeriod" in the request doesn't provide a correct range. The range can be too long with respect to the maximum possibile duration supported by the platform. Or startDate/endDate are not choerent with the API subscription. + value: + status: 422 + code: ENERGY_FOOTPRINT_NOTIFICATION.TIME_PERIOD_OUT_OF_RANGE + message: The requested time period for the evaluation is not a valid range. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1.md b/original/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1.md new file mode 100644 index 0000000000000000000000000000000000000000..94ca122cd02f0527c58fd4acc5fbe7f40e779091 --- /dev/null +++ b/original/EnergyFootprintNotification/documentation/API_documentation/EFN_UserStory_UseCase_1.md @@ -0,0 +1,13 @@ + + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service Provider has a partnership with the Telco Operator and instantiates applications in different Edge Data Centers of the Telco Operator. These application instances, altogether, provide a Service offered to End Users that are also subscribers of the Telco Operator. The Service, with this configuration, offers better network performances to the End Users. Service Provider wants to know the E2E energy consumption and CO2 emission of its Service in a certain period of time. A system of the Service Provider invokes the Energy Footprint Notification API to get the above-mentioned information. The reported energy consumption and CO2 emissions consider the energy used to run the instances of those applications in the Data Centers and the energy consumption along the network to provide the Service (e.g., RAN and Core Network consumption) in the specified period of time.| M | +|Roles, Actor(s) and scope|• Service Provider: role of EFN API consumer
                                                                      API Provider: role of EFN API provider
                                                                      • Operator Platform ([EdgeCloud/documentation/SupportingDocuments/Edge terminology/edge_terminology.md at main · camaraproject/EdgeCloud](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/Edge%20terminology/edge_terminology.md)): role of Service host
                                                                      • End User: both Teclo Operator's subscribers and Service Provider customer, role of Service consumer
                                                                      • Scope: Computing Services (OGW Taxonomy)| M | +|NF Requirements|NA| O | +|Pre-conditions|• The Service Provider onboarded applications on the Operator Platform
                                                                      • The Service Provider requested the deployment of some instances of those applications
                                                                      • The Service Provider identifies the Services as collection of application instances
                                                                      • The Service provided by those instances is up and running.
                                                                      • The End Users are consuming the Service| M | +|Begins when|The API Consumer invokes the EFN API to get the Energy consumption of the Service, composed by a set of application instances, in a specific time period.| M | +|Step 2|The API Provider returns the overall Energy consumption of the Service in that specific time period.| M| +|Step 4|The API Consumer invokes the EFN API to get the Carbon footprint of the Service, composed by a set of application instances, in a specific time period.| M | +|Step 5|The API Provider returns the Carbon footprint of the Service in that specific time period.| M| +|Post-conditions|The Service Provider is aware of the Energy consumption and of the Carbon footprint of the Service in the selected time periods| M | diff --git a/original/EnergyFootprintNotification/documentation/API_documentation/README.MD b/original/EnergyFootprintNotification/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/EnergyFootprintNotification/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist.md b/original/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ced5257eb6d2b032dfb49925533c19a0f815fe49 --- /dev/null +++ b/original/EnergyFootprintNotification/documentation/API_documentation/energy-footprint-API-Readiness-Checklist.md @@ -0,0 +1,28 @@ + + +# API Readiness Checklist + +Checklist for API energy-footprint-notification 0.1.0 in r1.3 + + + +| Nr | API release assets | alpha | release-candidate | initial
                                                                      public | stable
                                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/energy_footprint_notification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | 0.1.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/EFN_UserStory_UseCase_1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [Test-EC](/code/Test_definitions/energy-footprint-notification-calculateEnergyConsumption.feature), [Test-CF](/code/Test_definitions/energy-footprint-notification-calculateCarbonFootprint.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101707/EnergyFootprintNotification+API+description) | + + + + + diff --git a/original/EnergyFootprintNotification/documentation/SupportingDocuments/README.MD b/original/EnergyFootprintNotification/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/EnergyFootprintNotification/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/HighThroughputElasticNetworks/README.md b/original/HighThroughputElasticNetworks/README.md new file mode 100644 index 0000000000000000000000000000000000000000..dd64bda19a35ea02830e637b4e39aab7b6f5f64d --- /dev/null +++ b/original/HighThroughputElasticNetworks/README.md @@ -0,0 +1,39 @@ + + + + + + + + + +# HighThroughputElasticNetworks + +Sandbox API Repository to describe, develop, document, and test the HighThroughputElasticNetworks Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/wQAkAw) + +## Scope + +* Service APIs for “HighThroughputElasticNetworks” (see APIBacklog.md) +* The API provides the customer with the ability to: + * This API provides scheduling ability of huge data transmission in network. It can calculate load-balancing paths automatically with given time duration, total data amount and bandwidth limit, and satisfy huge data transmission requirements with dynamic and elastic bandwidth allocation algorithms, tidal-traffic-aware segment list adjustment and SRv6 multiple segment list technology.
                                                                      This API is designed for large enterprises requiring efficient network bandwidth management. It dynamically adjusts and optimizes bandwidth utilization to handle high-volume data transmission scenarios such as video conferences, large file transfers, and cloud resource access. By leveraging advanced technologies, it ensures seamless and efficient data flow across different time periods. This API is ideal for organizations that need robust solutions to manage substantial data transfers, ensuring high performance and reliability in demanding network environments.
                                                                      This API is suitable for customers in industries with massive data transfer requirements, such as Cross-cloud backup, model training at intelligent compute centers, video editing, and scientific computing. For example, the Five-hundred-meter Aperture Spherical radio Telescope (FAST), located in GuiZhou province of China, could generate more than 10 PB of observational data per year. By calling this API, users can dynamically adjust bandwidth and elastically orchestrate network resources according to their specific requirements for bandwidth, latency, and file size. This capability facilitates the efficient and expedient transmission of large observational datasets within short timeframes. In subsequent applications of the API, developers can set multiple groups of input parameters as standard configuration files, enabling quick selection and application.

                                                                      Input:
                                                                      1. Bandwidth Requirement: Time-segmented bandwidth requirements (can include multiple time points)
                                                                      2. Bandwidth Requirement Type: Upload bandwidth, download bandwidth, two-way bandwidth Service
                                                                      3. Latency Requirement: Latency guarantee requirement range
                                                                      4. File Requirements: Size of files to be transmitted
                                                                      5. Guarantee Requirements: Bandwidth guarantee and load sharing requirements

                                                                      Output:
                                                                      1. Success or failure
                                                                      2. Estimation of transmission rate by time segment
                                                                      3. Estimated transmission duration,
                                                                      4. Statistical conclusions after successful transmission1. Estimation of transmission rate by time segment
                                                                      5. (optional) any conditions required for the operator to meet the request (e.g. a particular entry point to the network must be used). +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: !! tbd + * [Registration / Join](https://wiki.camaraproject.org/x/TQAG) !! Update this link with your meeting registration/join link + * Minutes: Access [meeting minutes] !! update this link to your wiki page using the "Share" link +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/HighThroughputElasticNetworks/code/API_definitions/README.MD b/original/HighThroughputElasticNetworks/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/HighThroughputElasticNetworks/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/HighThroughputElasticNetworks/documentation/API_documentation/README.MD b/original/HighThroughputElasticNetworks/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/HighThroughputElasticNetworks/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/HighThroughputElasticNetworks/documentation/SupportingDocuments/README.MD b/original/HighThroughputElasticNetworks/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/HighThroughputElasticNetworks/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/HomeDevicesQoD/README.md b/original/HomeDevicesQoD/README.md new file mode 100644 index 0000000000000000000000000000000000000000..84ff97ef6781f32b6a0e1ab1c1ea64a465a42a8f --- /dev/null +++ b/original/HomeDevicesQoD/README.md @@ -0,0 +1,62 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#283](https://github.com/camaraproject/APIBacklog/issues/283) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase D – Repository With Reviewed Release](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# HomeDevicesQoD + +Sandbox API Repository to describe, develop, document, and test the HomeDeviceQoD Service API. The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/4TLe) + +## Scope +* Service APIs for “HomeDevicesQoD” (see APIBacklog.md) +* It provides the customer with the ability to: + * change, on demand, the desired QoS behaviour for the IP traffic corresponding to a specific user home device. +* Describe, develop, document and test the APIs +* Started: October 2022 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/r1.2) (Fall24), with the following API versions: + * **home-devices-qod v0.4.0** + [[YAML]](https://github.com/camaraproject/HomeDevicesQoD/blob/r1.2/code/API_definitions/home-devices-qod.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/r1.2/code/API_definitions/home-devices-qod.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/r1.2/code/API_definitions/home-devices-qod.yaml) +* The latest public release is always available here: https://github.com/camaraproject/HomeDevicesQoD/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/HomeDevicesQoD/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/HomeDevicesQoD/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://teams.microsoft.com/l/meetup-join/19%3ameeting_NzJkZDc4MjktNjU1YS00NzYxLWExNzgtZDlmNzI5MmMxMGNi%40thread.v2/0?context=%7b%22Tid%22%3a%229744600e-3e04-492e-baa1-25ec245c6f10%22%2c%22Oid%22%3a%22458d45b0-4ca7-41e2-a7b3-3d722abf4468%22%7d) (Microsoft Teams Meeting) + * Schedule: ~~bi-weekly~~ on demand(*), Thursday, 4:30pm CET. + * **(*)NOTE: The project is currently stable, so meetings will be scheduled according to the needs of the working group participants. Offline updates will be provided on the mailing list as needed instead.** If anyone in the working group would like to have one of the following meetings, please send an email to the list and/or open a new issue in the repository so that everyone can keep track of new topics to discuss. + * Minutes: Access [meeting minutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . + diff --git a/original/HomeDevicesQoD/code/API_definitions/home-devices-qod.yaml b/original/HomeDevicesQoD/code/API_definitions/home-devices-qod.yaml new file mode 100644 index 0000000000000000000000000000000000000000..4db9ec0634573007355772fbf4244eaeb2cdc94b --- /dev/null +++ b/original/HomeDevicesQoD/code/API_definitions/home-devices-qod.yaml @@ -0,0 +1,362 @@ +openapi: 3.0.3 +info: + title: Home Devices QoD + description: | + Service Enabling Network Function API for *QoS-on-demand* (QoD) control applied to devices connected to the user's home network. API clients can request to change, on demand, the desired QoS behaviour for the IP traffic corresponding to a specific user home device. The QoS behaviour is determined by the Service Class provided by the API Client, which is mapped to a DSCP value according to [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines. + + # Introduction + + It may be useful for application developers to request on-demand QoS behaviours (service classes) to be configured at the user's home WiFi access point to ensure the required quality of experience for those services/applications running on a specific home device. + + For example, the QoD control capability could be useful in scenarios such as: + + - A user using head-mounted display device for VR/AR applications. VR/AR applications require high bandwidth for the big amount of data to be streamed. + - A user using VoIP application in a home device. Lower latency improves call quality or avoids dropped calls. + + Generally speaking, QoS on demand may improve the qualty of experience for real time services like Videocomms, Cloud Gaming and Virtual Reality. + + ![Videocomms DSCP usage example](https://raw.githubusercontent.com/camaraproject/HomeDevicesQoD/main/documentation/API_documentation/resources/videocomm_dscp_example.png) + + # Relevant terms and definitions + + - **Home Device**: + User device connected to the user's home network. + + - **Service Class**: + A statement of the required QoS characteristics of a traffic aggregate. Conceptually, a service class refers to applications with similar characteristics and performance requirements. + + - **DSCP**: + *Differentiated Services (DiffServ) Code Point*. DiffServ is a simple and scalable mechanism for classifying and managing network traffic and providing quality of service (QoS) on IP networks. The DSCP value will be used to classify the traffic of the target home device in order to be treated accordingly. + + # API Functionality + + This API allows to third party clients to set, on demand, the desired QoS behaviour (service class) associated to the traffic of the device connected to the user's home network that matches the input criteria provided. The device traffic is classified (by DSCP) and treated accordingly. + + - **NOTE: The scope of the API is as follows**: + - QoS treatment is applied to a target user device **only within the user's home network** (i.e., between the device and the home router) + - QoS treatment **only applies to downstream IP traffic** (i.e., from the home router to the target device) + - QoS treatment **only applies to home devices using WiFi access** (i.e., home router WiFi interface) + + The API provides a single endpoint/operation: + + - Set the desired QoS behaviour for a user home device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details on how a client requests an access token. Please refer to Identify and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the Profile. + + Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + In the case of the Home Devices QoD API scenario and according to the API definition, 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This can be done via IP-based authentication (i.e. using the public IP of the device in this case). + + The 3-legged access of the Home Devices QoD API could also be combined with end-user consent management, depending on the legal basis applied. User consent would be required before personal data is processed by API clients for a specific purpose. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.4.0 + x-camara-commonalities: 0.4.0 +servers: + - url: "{apiRoot}/home-devices-qod/v0.4" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /qos: + put: + summary: Set the desired QoS behaviour for a user home device + description: | + Set the desired QoS behaviour for the traffic corresponding to the user home device matching the input criteria. **QoS behaviour is determined by the service class provided by the API Client. Setting `standard` service class restores default traffic treatment for the target home device.** + + - The operation is executed for the user whose `sub` is in the access token used to call this endpoint, and for the home network also deducted from the information included in the access token. + - The target user device is identified by the internal IP address of that device in the home network. + - In case there is no device matching the input criteria, the operation returns a 404 error. + tags: + - Home Devices QoD + operationId: setQos + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/QosOnDemandUpdate" + example: + serviceClass: real_time_interactive + ipAddress: 192.168.1.27 + required: true + responses: + "204": + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + description: Requested QoS passed all validations and was applied + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/setQosPermissionDenied403" + "404": + $ref: "#/components/responses/setQosNotFound404" + "409": + $ref: "#/components/responses/setQosConflict409" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/setQosServiceUnavailable503" + "504": + $ref: "#/components/responses/Generic504" +components: + schemas: + QosOnDemandUpdate: + type: object + description: Payload to change the QoS behaviour associated to a home device. + required: + - serviceClass + - ipAddress + properties: + serviceClass: + type: string + description: | + The name of the service class requested by the API client. It is associated with QoS behaviours optimised for a particular application type. Each service class is mapped to a DSCP value according to [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines. The DSCP value is used to classify the target home device's traffic so that it can be treated accordingly (i.e. to meet its QoS needs). + + The following service classes are supported: + + | Service Class Name | DSCP Name | DSCP value (decimal) | DCSP value (binary) | Application Examples | + |-----------------------|-----------|----------------------|---------------------|-----------------------------------------------| + | Real-Time Interactive | CS4 | 32 | 100000 | Video conferencing and Interactive gaming | + | Multimedia Streaming | AF31 | 26 | 011010 | Streaming video and audio on demand | + | Broadcast Video | CS3 | 24 | 011000 | Broadcast TV & live events | + | Low-Latency Data | AF21 | 18 | 010010 | Client/server transactions Web-based ordering | + | High-Throughput Data | AF11 | 10 | 001010 | Store and forward applications | + | Low-Priority Data | CS1 | 8 | 001000 | Any flow that has no BW assurance | + | Standard | DF(CS0) | 0 | 000000 | Undifferentiated applications | + enum: + - real_time_interactive + - multimedia_streaming + - broadcast_video + - low_latency_data + - high_throughput_data + - low_priority_data + - standard + example: real_time_interactive + ipAddress: + type: string + format: ipv4 + description: Internal IP address of the connected device in the LAN. + example: 192.168.1.27 + ErrorInfo: + type: object + required: + - message + - status + - code + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials + setQosPermissionDenied403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: User home network cannot be deducted from access token context + setQosNotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + NotFound: + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found + NoDeviceMatch: + value: + status: 404 + code: DEVICE_NOT_FOUND + message: No connected device found for the input criteria provided + setQosConflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Conflict: + value: + status: 409 + code: CONFLICT + message: Conflict with the current state of the target resource + TooManyDevices: + value: + status: 409 + code: HOME_DEVICES_QOD.TOO_MANY_DEVICES + message: Exceeded the maximum quantity of devices with non-default QoS behaviour + RssiBelowThreshold: + value: + status: 409 + code: HOME_DEVICES_QOD.RSSI_BELOW_THRESHOLD + message: RSSI from device is below allowed threshold + QosTooHigh: + value: + status: 409 + code: HOME_DEVICES_QOD.QOS_TOO_HIGH + message: Requested QoS is higher than the maximum QoS allowed + OccupancyAboveThreshold: + value: + status: 409 + code: HOME_DEVICES_QOD.OCCUPANCY_ABOVE_THRESHOLD + message: The occupancy is above the allowed threshold + NotConnectedToRequiredInterface: + value: + status: 409 + code: HOME_DEVICES_QOD.NOT_CONNECTED_TO_REQUIRED_INTERFACE + message: Device is not connected to the required interface (e.g. WiFi 5GHz interface) + NotSupportedRequiredInterface: + value: + status: 409 + code: HOME_DEVICES_QOD.NOT_SUPPORTED_REQUIRED_INTERFACE + message: Device does not support required interface (e.g. WiFi 5GHz interface) + QosAlreadySetToDefault: + value: + status: 409 + code: HOME_DEVICES_QOD.QOS_ALREADY_SET_TO_DEFAULT + message: Device QoS is already set to default value + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: Server error + setQosServiceUnavailable503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Unavailable: + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable + RouterOffline: + value: + status: 503 + code: HOME_DEVICES_QOD.ROUTER_OFFLINE + message: Router is not online. Try it later + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: Request timeout exceeded + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + securitySchemes: + openId: + description: | + OpenID Connect 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This can be done via IP-based authentication (i.e. using the public IP of the device in this case). + + The 3-legged access of the Home Devices QoD API could also be combined with end-user consent management, depending on the legal basis applied. User consent would be required before personal data is processed by API clients for a specific purpose. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration +security: + - openId: + - home-devices-qod:qos:write +tags: + - name: Home Devices QoD + description: QoD control operations for home devices +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/HomeDevicesQoD diff --git a/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist.md b/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..8cb3bf19018dc3319a14f06ed87d4ccf4a05744d --- /dev/null +++ b/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-API-Readiness-Checklist.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for home-devices-qod 0.4.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                      public | stable
                                                                      public | Status | Comments | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [home-devices-qod.yaml](/code/API_definitions/home-devices-qod.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded in [API definition](/code/API_definitions/home-devices-qod.yaml) | +| 6 | User stories | O | O | O | M | Y | [home-devices-qod-User-Stories.md](/documentation/API_documentation/home-devices-qod-User-Stories.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [home-devices-qod.feature](/code/Test_definitions/home-devices-qod.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [home-devices-qod.feature](/code/Test_definitions/home-devices-qod.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/xxx) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Comments column, provide the link to the asset once available, and any other relevant comments. + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: [API Readiness Checklist](https://wiki.camaraproject.org/x/HQBFAQ) diff --git a/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories.md b/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories.md new file mode 100644 index 0000000000000000000000000000000000000000..19ed9e19e7a054d14b78c6e402a0fc84a825e22e --- /dev/null +++ b/original/HomeDevicesQoD/documentation/API_documentation/home-devices-qod-User-Stories.md @@ -0,0 +1,11 @@ +**User Story: Configure traffic profile (DSCP)** +
                                                                      + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service) specific QoS behaviours (service classes) to be configured at my end-user's home WiFi access point to ensure the required quality of experience I need for my service/app. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                      **Actors:** Application service providers, hyperscalers, application developers.
                                                                      **Scope:** Configure QoS behaviours to ensure needed quality of experience for a given device within a residential LAN. The expected behaviour is that the target device is the same device where the app is running. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                      1. The end-user is connected to a residential WiFi access point.
                                                                      2. The end-user is running an application/service developed by the customer (application developer) that includes calls to the API.
                                                                      3. Security and privacy requirements are fulfilled as defined in Commonalities.
                                                                      | +| ***Activities/Steps*** | **Starts when:** The server/backend service calls the API specifying the service class required and the target device.
                                                                      **Ends when:** The requested QoS behaviour (service class) has been configured and the server/backend has being informed about it.
                                                                      | +| ***Post-conditions*** | Service class is applied and customer (application developer) app/service continues.
                                                                      Note that default QoS behaviour could be restored on back-end side at a given frequency (e.g. daily) or on demand by customer doing another call to the API.| +| ***Exceptions*** | Several exceptions might occur during the Home Devices QoD API operations
                                                                      • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                      • Invalid input: Not valid input data to invoke operation (e.g. invalid IP address, invalid service class, etc).
                                                                      • Denied by carrier: QoS behaviour cannot be implemented (already too many QoS behaviours configured, device is not connected to the required interface, etc), Server error, Service unavailable, request time exceeded, etc.
                                                                      | diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17.md new file mode 100644 index 0000000000000000000000000000000000000000..6cccf4217734933ff7155f97d4734f6a55194b25 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-17.md @@ -0,0 +1,41 @@ +# Camara Home Devices QoD meeting + +*17/11/2022* + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Anne Matthieu (Orange) +* Flury Thibaud (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes: [https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Kick-off follow-up meetings +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Kick-off** | | +| | Telefonica provides a general view of the API value proposition and a general review of the API YAML definition already uploaded to the github repository. Waiting feedback from partners | +| **Recap & Recent Updates** | | +| |
                                                                      • Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                      • Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues) 
                                                                      • Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls)
                                                                      | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                                                                    7. [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| **New Issues** | | +| | none | +| **AOB** | | +| | Next Home Devices QoD community call on Nov 24th, UTC 16:00, CET 17:00 | diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24.md new file mode 100644 index 0000000000000000000000000000000000000000..652b45f2b3bf1bdd4e489b6226b4f89b31a37c2a --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-11-24.md @@ -0,0 +1,48 @@ +# Camara Home Devices QoD meeting + +## Meeting Information +**Meeting Date:** 24/11/2022 + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Sylvain Morel (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes link: +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                      +Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                      +Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +## Discussion Items + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                      • DT will be joining to github repository and will be participating soon in the API definition. Waiting contact person/s from DT to invite them to participate.
                                                                      • Orange request to provide some further information about the user stories being considered by TEF. And they propose to upload the user stories information following the corresponding template as done for [Carrier Billing API](https://github.com/alabajnaid/CarrierBillingCheckOut/blob/api_user_stories/documentation/API_documentation/carrier_billing_user_stories.md). They will use it for internal marketing purposes having a better understanding of what it is being proposed for Home Devices QoD API.
                                                                      • TEF request some feedback from Orange regarding the technical feasibility of the API from their side and/or some feedback on the API definition itself. | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                                                                      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| **New Issues** | | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) Aligment with API Design Guidelines Commonality. Being addressed in PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)
                                                                      • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md) | +| **AOB** | | +| | Next Home Devices QoD community call on Dic 1st, UTC 16:00, CET 17:00 | + +## Next Steps + +* TEF will upload a 1st draft of user stories document in https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/API_documentation +* Orange to provide feedback on user stories and API definition. \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01.md new file mode 100644 index 0000000000000000000000000000000000000000..d4621dcc6280068ac2c0a9af6c15411264341f51 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2022-12-01.md @@ -0,0 +1,48 @@ +# Camara Home Devices QoD meeting + +## Meeting Information +**Meeting Date:** 01/12/2022 + +## Attendees + +* Jesús Peña (Telefonica) +* Josue Igual (Telefonica) +* Eber Augusto (Telefonica) +* Mona Mokhber (Telefonica) +* Sylvain Morel (Orange) +* Robert Ludovic (Orange) + +Home Devices QoD minutes link: +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update on issues +* AOB + +Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                        +Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                        +Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +## Discussion Items + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                        • Still waiting technical contacts from DT to get them involved in github project and API design. PING done to DT this week. They are working on it
                                                                        • No further updates... | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                          The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101). API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers. Is anyone interested in joining the maintainers group? In case you are, please comment on this issue.
                                                                        • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD) | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) Aligment with API Design Guidelines Commonality. Being addressed in PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)
                                                                        • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md) | +| **New Issues** | | +| | [#9](https://github.com/camaraproject/HomeDevicesQoD/issues/9) Upload first version of user stories doc in API documentation. Being addressed in PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10).

                                                                          Comments received from Orange (Robert Ludovic) already answered in the PR itself. It has been agreed to include [some additional clarifications](https://github.com/camaraproject/HomeDevicesQoD/pull/10#issuecomment-1333796244) in the user story doc before merge it. | +| **AOB** | | +| | Next Home Devices QoD community call on Dic 15th, UTC 16:00, CET 17:00 (Dic 8th is bank holiday in Spain) | + +## Next Steps + +* TEF to update PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10) with agreed changes. diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12.md new file mode 100644 index 0000000000000000000000000000000000000000..f8f805071751025e68efa834b8044b96d179416d --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-12.md @@ -0,0 +1,56 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 12/01/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Robert Ludovic (Orange) +* Rafal Artych (DT) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                                          +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                          +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                          +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                        • MERGED PR [12](https://github.com/camaraproject/HomeDevicesQoD/pull/12) Fix version number typo in api definition -> Fix version number typo in api definition YAML file as it should be v0.1.0 (representing the first API proposal) and not yet v1.0.0.

                                                                        • API version v0.1.0 is merged in `main` branch including API definition YAML file, user stories doc file (PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10)) and API documentation file (PR [#15](https://github.com/camaraproject/HomeDevicesQoD/pull/15)). This API version corresponds to the one TEF will bring to MWC.

                                                                        • A new branch `dev-v0.2.0` has been created including some minor changes: 1) "*Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*" (PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) replacing PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)) and 2) "*403 specific API error when User home network cannot be deducted from access token*" (PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14)). Furhter changes in API definition (if any) will be addressed in this version or subsequent versions.

                                                                        • Working with Noel Wirzius to get technical contact/s from DT and to get them involved in github project and API design. He was expected to provide information in the coming days but Rafal Artych (representing DT) has joined the call Today. He already have access to github repository and is subscribed to the mailing list. | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101).
                                                                          API design would include an anonymised ID is it is eventually agreed on the corresponding CAMARA Commonalities track. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                                                                          To be CLOSED as soon DT contact/s are 100% confirmed.
                                                                          • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                                                                          | +| | [#8](https://github.com/camaraproject/HomeDevicesQoD/issues/8) ~~Aligment with API Design Guidelines Commonality.~~
                                                                          CLOSED. Addressed in PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) already MERGED (which replaced PR [#7](https://github.com/camaraproject/HomeDevicesQoD/pull/7)).
                                                                          • [API Design Guidelines Commonality](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md)
                                                                          | +| | [#9](https://github.com/camaraproject/HomeDevicesQoD/issues/9) ~~Upload first version of user stories doc in API documentation~~
                                                                          CLOSED. Addressed in PR [#10](https://github.com/camaraproject/HomeDevicesQoD/pull/10) already MERGED. | +| **New Issues** | | +| | [#16](https://github.com/camaraproject/HomeDevicesQoD/issues/16) ~~Upload first version of API documentation~~
                                                                          CLOSED. Addressed in PR [#15](https://github.com/camaraproject/HomeDevicesQoD/pull/15) already MERGED. | +| **AOB** | | +| |
                                                                        • Next Home Devices QoD community call on Jan 19th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Get feedback from other CAMARA partners including Orange and DT after their internal promotion of the API. + * Robert Ludovic confirms that the API is not prioritized in Orange side for the short-term. Orange feedback on API and uses cases should be expected for the mid-term. + * Waiting DT potential feedback as soon as they manage the review the API information already uploaded to github. +* Move forward with CAMARA API milestones. + +
                                                                          + +> Mailinglist:
                                                                          Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                          The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19.md new file mode 100644 index 0000000000000000000000000000000000000000..4ae47803d9e537e3771dc4a2959b3ff02d51e296 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-01-19.md @@ -0,0 +1,52 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 19/01/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                                          +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                          +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                          +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                        • API doc updates for API version 0.2.0 being included in branch `dev-v0.2.0` (new issue [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18)). | +| **Open Issues** | | +| | [#2](https://github.com/camaraproject/HomeDevicesQoD/issues/2) ~~Pending API update related to CAMARA commonalities issue [#101](https://github.com/camaraproject/WorkingGroups/issues/101).~~
                                                                          CLOSED. The corresponding CAMARA Commonalities track has been closed with some agreements but not a unique traversal solution. Each API we work on will need to consider additional requirements (if any) to decide which identifiers makes the most sense. So far, in case of Home Devices QoD current definition, it's assumed user authentication (3-legged token). And the user and home network information are deducted from the information included in the access token. There is no user identifier filed included in the API request body. | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                                                                          To be CLOSED as soon DT contact/s are 100% confirmed.
                                                                          • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                                                                          Working with Noel Wirzius to get technical contact/s from DT and to get them involved in github project and API design. He was expected to provide information during this days. Still no confirmation received from him. So far Rafal Artych (representing DT) is joining weekly calls. He has confirmed that he is speaking with Noel already and next week they hope to be able to confirm who the contact person/s will be. | +| **New Issues** | | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                                                                          Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                                                                          • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                                                                          • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                                                                          | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                                                                          It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).
                                                                        | +| **AOB** | | +| |
                                                                      • Next Home Devices QoD community call on Jan 26th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Get the feedback DT may have about uses cases and API design. + * It will have to wait most likely until DT technical contact is confirmed. + +
                                                                        + +> Mailinglist:
                                                                        Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                        The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02.md new file mode 100644 index 0000000000000000000000000000000000000000..56fbcac8e80cb350e3ed3ce5883008c251778285 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-02.md @@ -0,0 +1,51 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 02/02/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) +* Vaishali Gupta (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                                        +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                        +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                        +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                      • Current project status will be reported to see the best way forward to meet the CAMARA API milestones.
                                                                      • The call frequency will be re-evaluated to see if every two weeks is better for now.
                                                                      • Our colleagues from DELL are joining the call for the first time. They belong to DELL engineering team and they are doing a preliminary overall evaluation of the CAMARA project and the more interesting API projects for them (like Home Devices QoD API in this case). According to Mike, for the moment they are not in position to provide feedback on the API design or API use cases.
                                                                      • Rafal can't confirm when DT will provide feeback on the API design or use cases. DT`s technical department is currently discussing this issue and will come back. In today's call Rafal brings some personal suggestions for the API definition. It is agreed to create a Github issue for each of them to track the discussion and link them to the required PR if it is eventually needed. | +| **Open Issues** | | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                                                                        To be CLOSED as soon DT contact/s are 100% confirmed.
                                                                        • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                                                                        Rafal can't confirm when the DT contact person(s) will be defined. He suggests to bring it up in the next SteerCo (next week). For the moment he will join the calls and keep the lights on. | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                                                                        Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                                                                        • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                                                                        • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                                                                        No further changes included last two weeks. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                                                                        It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                                                                        No updates on this one. Still not clear how it is going to be handled in CAMARA Commonalities.
                                                                      | +| **New Issues** | | +| | N/A | +| **AOB** | | +| |
                                                                    8. Next Home Devices QoD community call on Feb 9th, UTC 16:00, CET 17:00
                                                                        (*)_To be confirmed depending on the call frequency re-evaluation_
                                                                      | + + +## Next Steps + +* Get the feedback DT may have about uses cases and API design.
                                                                      (*)_It will most likely have to wait until DT technical contact(s) are confirmed._ + +
                                                                      + +> Mailinglist:
                                                                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15.md new file mode 100644 index 0000000000000000000000000000000000000000..dabd35b4acb4c054c9c33bbd003cb8e87de147e6 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-02-15.md @@ -0,0 +1,53 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 15/02/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                                    9. The current status of the project was reported to SteerCo last week (including the matter of the DT technical contacts).
                                                                    10. The call frequency will be set to every two weeks (same time slot). This is more appropriate for the time being, until DT’s engagement in the API discussions.
                                                                    11. In the previous call Rafal brought some personal suggestions for the API definition. As agreed, a new Github issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) has been created to track the discussion and link it to the required PR if it is eventually needed. | +| **Open Issues** | | +| | [#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers.
                                                                      To be CLOSED as soon DT contact/s are 100% confirmed.
                                                                      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                                                                      Rafal has no news in the matter of DT's technical contacts. No news is expected until after the Mobile World Congress. | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                                                                      Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19). Updates included so far corresponds to:
                                                                      • PR [#13](https://github.com/camaraproject/HomeDevicesQoD/pull/13) "*dev-v0.2.0 - Aligment with API Design Guidelines Commonality - Add "status" field in error definitions*".
                                                                      • PR [#14](https://github.com/camaraproject/HomeDevicesQoD/pull/14) "*Add 403 specific API error when User home network cannot be deducted from access token*".
                                                                      No further changes included in last two weeks. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                                                                      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                                                                      No updates on this one. Still not clear how it is going to be handled in CAMARA Commonalities.
                                                      | +| **New Issues** | | +| | [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) Reduction of network-specific terminolgy/acronyms
                                                      This issue is actually aligned with Commonalities issue [#108](https://github.com/camaraproject/WorkingGroups/issues/108) and PR [#120](https://github.com/camaraproject/WorkingGroups/pull/120). From TEF side it is being validated inernally with the technical and business teams and a solution aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) is being considered. | +| **AOB** | | +| |
                                                    6. Next Home Devices QoD community call on Mar 2nd, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Telefonica to provide a proposal to address issue #23. +* Get the feedback DT may have about uses cases and API design.
                                                      (*) _It will have to wait until DT technical contact(s) are confirmed. Not before MWC._ + +
                                                      + +> Mailinglist:
                                                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16.md new file mode 100644 index 0000000000000000000000000000000000000000..4296d1b855ac8411a5c52e50fe1c542da80fc210 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-16.md @@ -0,0 +1,54 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 16/03/2023 + +### Attendees + +* Jesús Peña (Telefonica) +* Emilio Abraham Garrido García (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                    7. Project adaptation to release/versioning guidelines agreed in Commonalities is done (issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27)).
                                                    8. "Service class" included in [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) as relevant API term to update commonalities glossary with HomeDevicesQoD-subproject relevant terms.
                                                    9. New API definition aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) has been included in release v0.2.0 (it resolves issue[#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23)).
                                                    10. Update API documentation according to release 0.2.0 API version stopped until a final agreement is reached in Commonalities issue [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164)| +| **Open Issues** | | +| | ~~[#3](https://github.com/camaraproject/HomeDevicesQoD/issues/3) Maintainers~~~.
                                                      CLOSED. Rafal has been added as a maintainer (PR [#26](https://github.com/camaraproject/HomeDevicesQoD/pull/26).), as he is the contact person from DT who is actively involved in the project. And this issue has been closed, as there's no point in discussing it any further.
                                                      • [Current Maintainers](https://github.com/camaraproject/HomeDevicesQoD/blob/main/MAINTAINERS.MD)
                                                      | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                                                      ~~Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19)~~.
                                                      PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19) has been MERGED to `dev-v0.2.0` branch with current documentation status (i.e. NOT including Doc changes related to issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) and PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25)).
                                                      This is part of the process described in issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) to adapt the project to the release/versioning policy agreed in Commonalities, i.e. the `main` branch is assumed to be the latest. Documentation work corresponding to API release v0.2.0 (when resumed) will be done against the `main' branch until release v0.2.0 is agreed to be closed.

                                                      On the other hand, there is a new issue in the Commonalities project [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164) that affects this. Basically because the way the CAMARA APIs are documented is being rethought. It is proposed not to have separate documentation at all, but to embed all documentation in the OAS definition itself (YAML). The Home Devices QoD spec file is already quite self-documented, so I'll wait for the final agreement in Commonalities to complete the documentation for release 0.2.0 to avoid unnecessary overhead. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                                                      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                                                      Added "Service Class" as a representative term for this API.| +| | ~~[#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) Reduction of network-specific terminolgy/acronyms~~
                                                      This issue is actually aligned with Commonalities issue [#108](https://github.com/camaraproject/WorkingGroups/issues/108) and PR [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                                                      CLOSED. On the TEF side, after internal validation with the technical and business teams, a new API definition aligned with [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) was provided in PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25). The changes made were approved by Rafal (DT) and Robert Ludovic (Orange) and the PR was MERGED. | +| **New Issues** | | +| | ~~[#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) Adapt project to release/versioning guidelines agreed in Commonalities~~
                                                      Commonalities track: https://github.com/camaraproject/WorkingGroups/pull/123.

                                                      CLOSED already. Steps accomplished:
                                                      • ~~PR to merge v0.1.0 changelog into the main branch.~~ >> DONE. PRs [#28](https://github.com/camaraproject/HomeDevicesQoD/pull/28) (added CHANGELOG) and [#29](https://github.com/camaraproject/HomeDevicesQoD/pull/29) (typo fix)
                                                      • ~~The merge commit from PR will be tagged as v0.1.0, and will get the v0.1.0 release branch.~~ >> DONE https://github.com/camaraproject/HomeDevicesQoD/releases
                                                      • ~~Merge the dev-v0.2.0 branch into main, so that it contains the latest stable API definition state as agreed.~~ >> DONE. PR [#30](https://github.com/camaraproject/HomeDevicesQoD/pull/30)
                                                      • ~~Update README.md accordingly..~~ >> DONE. PR [#31](https://github.com/camaraproject/HomeDevicesQoD/pull/31)
                                                      | +| **AOB** | | +| |
                                                    11. Next Home Devices QoD community call on Mar 30th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create a new PR to align API spec files with pending traversal Commonalities issues like: CamelCase usage (issue [#157](https://github.com/camaraproject/WorkingGroups/issues/157)), error schema definitions (issue [#151](https://github.com/camaraproject/WorkingGroups/issues/151)), API documentation (issue [#164](https://github.com/camaraproject/WorkingGroups/issues/164)), etc... +* When this is done, generate the first stable API release and continue with the CAMARA milestones to complete it, as no further functionality will be added for the time being. + +
                                                      + +> Mailinglist:
                                                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org \ No newline at end of file diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30.md new file mode 100644 index 0000000000000000000000000000000000000000..7f79904770437e824fbdc91d022eeb8cf812f819 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-03-30.md @@ -0,0 +1,56 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 30/03/2023 + +### Attendees + +* Mona Mokhber (Telefonica) +* Diego Rivera Nuñez (Telefonica) +* Eber Marins (Telefonica) +* Christian Duran Gonzalez (Telefonica) +* Rafal Artych (DT) +* "Mike" - Mihai Lazar (DELL) + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                    12. [#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33) created to align the API with the new guideline agreements| +| **Open Issues** | | +| | [#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) Update API documentation according to v0.2.0 API version
                                                      ~~Being addressed in PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19)~~.
                                                      PR [#19](https://github.com/camaraproject/HomeDevicesQoD/pull/19) has been MERGED to `dev-v0.2.0` branch with current documentation status (i.e. NOT including Doc changes related to issue [#23](https://github.com/camaraproject/HomeDevicesQoD/issues/23) and PR [#25](https://github.com/camaraproject/HomeDevicesQoD/pull/25)).
                                                      This is part of the process described in issue [#27](https://github.com/camaraproject/HomeDevicesQoD/issues/27) to adapt the project to the release/versioning policy agreed in Commonalities, i.e. the `main` branch is assumed to be the latest. Documentation work corresponding to API release v0.2.0 (when resumed) will be done against the `main' branch until release v0.2.0 is agreed to be closed.

                                                      On the other hand, there is a new issue in the Commonalities project [Revisit API documentation template to reduce redundancy #164](https://github.com/camaraproject/WorkingGroups/issues/164) that affects this. Basically because the way the CAMARA APIs are documented is being rethought. It is proposed not to have separate documentation at all, but to embed all documentation in the OAS definition itself (YAML). The Home Devices QoD spec file is already quite self-documented, so I'll wait for the final agreement in Commonalities to complete the documentation for release 0.2.0 to avoid unnecessary overhead. | +| | [#20](https://github.com/camaraproject/HomeDevicesQoD/issues/20) Update commonalities glossary with HomeDevicesQoD-subproject relevant terms
                                                      It is related to Commonalities issue [#120](https://github.com/camaraproject/WorkingGroups/pull/120).

                                                      Added "Service Class" as a representative term for this API.| +| **New Issues** | | +| | [#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33) Align API spec format with the latest Commonalities agreements
                                                      This issue is to align API spec format with the latest Commonalities agreements
                                                    13. Commonalities - adjust the error `status` field, which will eventually be an integer (not a patterned string): PR [#145](https://github.com/camaraproject/WorkingGroups/pull/145).
                                                    14. Commonalities - adjust the schema references in the errors responses and apply the agreed solution: Issue [#151](https://github.com/camaraproject/WorkingGroups/issues/151) & PR [#162](https://github.com/camaraproject/WorkingGroups/pull/162).
                                                    15. Commonalities - change the format of the API fields to lowerCamelCase: Issue [#157](https://github.com/camaraproject/WorkingGroups/issues/157), Discussion [#169](https://github.com/camaraproject/WorkingGroups/discussions/169) & PR [#171](https://github.com/camaraproject/WorkingGroups/pull/171).
                                                      The changes were approved by Ludovic (Orange) pending to be approved by Rafal (DT) in order to get merged. | +| **AOB** | | +| |
                                                    16. Next Home Devices QoD community call on Apr 13th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* [PR#34](https://github.com/camaraproject/HomeDevicesQoD/pull/34) to get approved by pending reviewers and will be merged and closed afterwards (along with its related [issue#33](https://github.com/camaraproject/HomeDevicesQoD/issues/33)) + +* The note from last meeting is still pending: +***"Generate the first stable API release and continue with the CAMARA milestones to complete it, as no further functionality will be added for the time being."*** + +* No furthur issues were discussed during the meeting. + +
                                                      + +> Mailinglist:
                                                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08.md new file mode 100644 index 0000000000000000000000000000000000000000..af956c607aa7631986b0ed5a90f5a2525c8c1d36 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-06-08.md @@ -0,0 +1,59 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 08/06/2023 + +### Attendees + +| Companies | Attendees | +| --------- | --------- | +| Telefónica | Jesús Peña, Eber Marins, Christian Duran | + +
                                                      + +**No other WG participants joined today's call, so these meeting notes are provided as an offline update for the record**... + +
                                                      + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +
                                                      + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +
                                                      + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                    17. Current project status: 2 open issues and no ongoing PRs.
                                                    18. Issue 18 "v0.2.0 - Update API documentation according to v0.2.0 API version" has been CLOSED. Addressed in PR #30 which has been already merged.
                                                    19. PR #40 "Creation of API readiness checklist document (Issue 39)" has been merged. It is related to open issue #39.
                                                    20. New issue #41 "WiFi QoS Mappings" | +| **Open Issues** | | +| |
                                                    21. ~~[#18](https://github.com/camaraproject/HomeDevicesQoD/issues/18) "v0.2.0 - Update API documentation according to v0.2.0 API version"~~
                                                      CLOSED. This issue was addressed in PR ~~[#38]((https://github.com/camaraproject/HomeDevicesQoD/pull/38))~~ which has already been merged. The PR updates the API documentation according to v0.2.0 API version definition, including changes from v0.1.0 release, and adds the documentation to the API definition as discussed in issue [#64](https://github.com/camaraproject/WorkingGroups/issues/164) of Commonalities. This PR is in line with what it is being done in other subprojects (such as [QualityOnDemand](https://github.com/camaraproject/QualityOnDemand/pull/151)).
                                                      • This was the only remaining change before closing and creating the v0.2.0 release on github.
                                                      | +| | [#39](https://github.com/camaraproject/HomeDevicesQoD/issues/39) "Generation of release v1.0.0"
                                                      Issue to validate and meet API readiness requirements to generate a first stable API release v1.0.0 from v0.2.0. No further functionality will be added to the API. The requirements in order to generate a release v1.0.0 in CAMARA APIs are being discussed in Commonalities (Issue [#139](https://github.com/camaraproject/WorkingGroups/issues/139)). The corresponding release v1.0.0 would be generated in the github project.
                                                      • ~~PR [#40](https://github.com/camaraproject/HomeDevicesQoD/issues/39) - "Creation of API readiness checklist document (Issue 39)"~~
                                                        MERGED. The "home_devices_qod_readiness_checklist.md" document with the API readiness status [is now available](https://github.com/camaraproject/HomeDevicesQoD/blob/main/documentation/API_documentation/home_devices_qod_readiness_checklist.md) as done in the [QualityOnDemand project](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoD-API-Readiness-Checklist.md)
                                                      • The requirement to fulfill step 5 ("API test cases and documentation") of the API Readiness checklist is being discussed in issue [#61](https://github.com/camaraproject/WorkingGroups/issues/61) of Commonalities. Need to confirm mandatory deliverable(s) and whether it is good enough to provide the ".feature" file or not.
                                                      | +| **New Issues** | | +| | [#41](https://github.com/camaraproject/HomeDevicesQoD/issues/41) "WiFi QoS Mappings"
                                                      Open by DT (Rafal), it is intended to refer to [RFC8325](https://datatracker.ietf.org/doc/html/rfc8325) in the documentation as the standard reference for WiFi downstream. From Telefonica's point of view, there is no need to do this as the current API design is not related to RFC8325 or IEEE 802.11 UP (User Priority). The current proposal is based on the DSCP value set in the user's home router to control the QoS behaviour of the target home device's IP traffic. And it has been defined the "service class" concept on top of DSCP to provide a developer-friendly design following RFC4594 recommendations. So existing documented service class mapping to DSCP should be sufficient. | +| **AOB** | | +| |
                                                    22. Next Home Devices QoD community call on June 21st, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create issue and PR to generate v0.2.0 release on github. +* Continue discussion on issue #39 "Generation of release v1.0.0".
                                                      • If providing a ".feature" file is confirmed as the minimum mandatory deliverable, then create PR to provide the ".feature" file as the API test cases definition.
                                                      +* Close discussion on issue #41 "WiFi QoS Mappings". + +
                                                      + +> Mailinglist:
                                                      Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                                      The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06.md b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06.md new file mode 100644 index 0000000000000000000000000000000000000000..857a65b417c9fd5f2a8e3fab2d1979d2a0e9dffc --- /dev/null +++ b/original/HomeDevicesQoD/documentation/MeetingMinutes/MOM-2023-07-06.md @@ -0,0 +1,55 @@ +# Camara Home Devices QoD meeting + +## Meeting Information + +> Meeting Date: 06/07/2023 + +### Attendees + +| Companies | Attendees | +| --------- | --------- | +| Telefónica | Jesús Peña, Christian Duran | +| LibertyGlobal | George Haddad | + +
                                                      + +### Agenda + +* Recap & Recent Updates +* Update on issues +* AOB + +Home Devices QoD minutes link:
                                                      +[https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/HomeDevicesQoD/tree/main/documentation/MeetingMinutes) + +
                                                      + +## Discussion Items + +- Repo: [https://github.com/camaraproject/HomeDevicesQoD](https://github.com/camaraproject/HomeDevicesQoD)
                                                      +- Issues: [https://github.com/camaraproject/HomeDevicesQoD/issues](https://github.com/camaraproject/HomeDevicesQoD/issues)
                                                      +- Pull Requests: [https://github.com/camaraproject/HomeDevicesQoD/pulls](https://github.com/camaraproject/HomeDevicesQoD/pulls) + +
                                                      + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap/Updates** | | +| |
                                                    23. Current project status: 2 open issues and no ongoing PRs.
                                                    24. Issue 44 "Generation of release v0.2.0" has been CLOSED. Release [v0.2.0](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/v0.2.0) is now available.
                                                    25. Issue #41 "WiFi QoS Mappings" has been CLOSED in view of the comments provided and the fact that there are no further objections.
                                                    26. Issue #39 "Generation of release v1.0.0" is ongoing. From release v0.2.0, work will begin to generate the first stable API version v1.0.0 by contributing with the API test cases definition.
                                                    27. New Issue #46 "Add option to apply QoD to subnets" | +| **Open Issues** | | +| | [#39](https://github.com/camaraproject/HomeDevicesQoD/issues/39) "Generation of release v1.0.0"
                                                      Issue to validate and meet API readiness requirements to generate a first stable API release v1.0.0 from v0.2.0. No further functionality will be added to the API.
                                                      • The requirement to fulfill step 5 ("API test cases and documentation") of the API Readiness checklist has been agreed in issue [#61](https://github.com/camaraproject/WorkingGroups/issues/61) of Commonalities. It has been confirmed that it is good enough to provide the ".feature" file.
                                                      | +| | ~~[#41](https://github.com/camaraproject/HomeDevicesQoD/issues/41) "WiFi QoS Mappings"~~
                                                      CLOSED in view of the comments provided and the fact that there are no further objections.
                                                      The current proposal is based on the DSCP value set in the user's home router to control the QoS behaviour of the target home device's IP traffic. And it has been defined the "service class" concept on top of DSCP to provide a developer-friendly design following RFC4594 recommendations. So existing documented service class mapping to DSCP should be sufficient. | +| | ~~[#44](https://github.com/camaraproject/HomeDevicesQoD/issues/44) "Generation of release v0.2.0"~~
                                                      CLOSED
                                                      Addressed in PR [#45](https://github.com/camaraproject/HomeDevicesQoD/pull/45) which has been already merged. Release [v0.2.0](https://github.com/camaraproject/HomeDevicesQoD/releases/tag/v0.2.0) is now available. | +| **New Issues** | | +| | [#46](https://github.com/camaraproject/HomeDevicesQoD/issues/46) "Add option to apply QoD to subnets"
                                                      Open by Cablelabs (Randy Levensalor), it is intended to suggest an API enhancement to apply QoD to home subnets.
                                                      This would be a new functionality, so formal procedure through GSMA OGW Product WS must be followed since GSMA is the one that manages priorities at the product level.
                                                      From Telefónica perspective, suggested feature is probably more appropriate for an internal Operator application, where the user has a "control panel" or similar to manage their home network resources, devices and configurations (including subnets). But in the CAMARA context, where Operator exposes APIs to third party developers, the subnet information may not be known/accessible to the developer (exposed information is limited).| +| **AOB** | | +| |
                                                    28. Next Home Devices QoD community call on July 20th, UTC 16:00, CET 17:00 | + + +## Next Steps + +* Create PR to provide the ".feature" file as the API test cases definition.
                                              + +
                                              + +> Mailinglist:
                                              Please subscribe if not yet done to the mailing list of the subproject here: [https://lists.camaraproject.org/g/sp-hdp](https://lists.camaraproject.org/g/sp-hdp)
                                              The list will be used for invitations and discussions between members of the sub project. The address is: sp-hdp@lists.camaraproject.org diff --git a/original/HomeDevicesQoD/documentation/SupportingDocuments/README.MD b/original/HomeDevicesQoD/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..38efecab2903648866bb8d5f867fab0e77ea71c6 --- /dev/null +++ b/original/HomeDevicesQoD/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/original/InHomeDeviceManagement/README.md b/original/InHomeDeviceManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9a5ae2ce77f7477c21a84ad03815812121b02947 --- /dev/null +++ b/original/InHomeDeviceManagement/README.md @@ -0,0 +1,42 @@ + + + + + + + + + +# InHomeDeviceManagement + +Sandbox API Repository to describe, develop, document, and test the InHomeDeviceManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQCxGw) + +## Scope + +* Service API(s) “InHomeDeviceManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: January 2026 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/EACpGw) + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/InHomeDeviceManagement/code/API_definitions/README.MD b/original/InHomeDeviceManagement/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/InHomeDeviceManagement/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/InHomeDeviceManagement/documentation/API_documentation/README.MD b/original/InHomeDeviceManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/InHomeDeviceManagement/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/InHomeDeviceManagement/documentation/SupportingDocuments/README.MD b/original/InHomeDeviceManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/InHomeDeviceManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTDeviceManagement/README.md b/original/IoTDeviceManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..0031dff5634d4b0df7942c212e498dcb1a82665d --- /dev/null +++ b/original/IoTDeviceManagement/README.md @@ -0,0 +1,43 @@ + + + + + + + + + +# IoTDeviceManagement + +Sandbox API Repository to describe, develop, document, and test the IoT Device Management Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/boCeBQ) + +## Scope + +* Service API(s) “IoTDeviceManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * manage communication functions, like activation and deactivation of voice, SMS, data services, and specific APNs, ensuring precise traffic control to prevent overload. + * manage device subscription state, perform operations such as adding, activating, suspending, restoring, deactivating, and deleting IoT cards. + * support real-time monitoring, provide visibility into the status of IoT cards, enabling continuous supervision and efficient control of service usage and status. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Tuesday, 13:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99489769217?password=b970b062-a3ef-4a58-95ed-2b15610d84fb) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/p4CgBQ) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/IoTDeviceManagement/code/API_definitions/README.MD b/original/IoTDeviceManagement/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/IoTDeviceManagement/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/IoTDeviceManagement/documentation/API_documentation/README.MD b/original/IoTDeviceManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTDeviceManagement/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTDeviceManagement/documentation/SupportingDocuments/README.MD b/original/IoTDeviceManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTDeviceManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTNetworkOptimization/README.md b/original/IoTNetworkOptimization/README.md new file mode 100644 index 0000000000000000000000000000000000000000..e34ff5677aa444750bbc6d720dd9558d2589b383 --- /dev/null +++ b/original/IoTNetworkOptimization/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# IoTNetworkOptimization + +Sandbox API Repository to describe, develop, document, and test the IoTNetworkOptimization Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYCzBw) +* [Provider Implementation](https://github.com/camaraproject/IoTNetworkOptimization_PI) + +## Scope + +* Service API(s) “IoTNetworkOptimization” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * activate network features for that specific fleet of IoT devices, e.g., energy saving features. +* Describe, develop, document, and test the API(s) +* Started: April 2025 + + + + + +## Release Information + +> [!NOTE] +> This repository has only pre-release versions available yet. Pre-releases are for testing and may change before public release. + +* **PREVIEW**: The latest pre-release is [r1.1](https://github.com/camaraproject/IoTNetworkOptimization/releases/tag/r1.1) (alpha), with the following API versions: + * **iot-network-optimization v0.1.0-alpha.1** + [[YAML]](https://github.com/camaraproject/IoTNetworkOptimization/blob/r1.1/code/API_definitions/iot-network-optimization.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/IoTNetworkOptimization/r1.1/code/API_definitions/iot-network-optimization.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/IoTNetworkOptimization/r1.1/code/API_definitions/iot-network-optimization.yaml) +* For changes see [CHANGELOG.md](https://github.com/camaraproject/IoTNetworkOptimization/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Wednesday 10:00 AM - 11:00 AM UTC (12:00 PM -13:00 PM CEST): [wiki Calandar](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi?view=week) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/T4CzBw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/IoTNetworkOptimization/code/API_definitions/README.MD b/original/IoTNetworkOptimization/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/IoTNetworkOptimization/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/IoTNetworkOptimization/code/API_definitions/iot-network-optimization.yaml b/original/IoTNetworkOptimization/code/API_definitions/iot-network-optimization.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f88b7de33b46f2c5c87f2e8200e05f8353d0d4ae --- /dev/null +++ b/original/IoTNetworkOptimization/code/API_definitions/iot-network-optimization.yaml @@ -0,0 +1,1071 @@ +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: IoT Network Optimization API + description: | + ## Overview + The IoT Network Optimization API provides the API Consumer with the + capabilities of activating IoT-specific features for a fleet of devices. + ## Introduction + The scenario a Service Provider that partners with a Telco Operator to + deploy IoT devices (e.g., sensors, trackers) across the Telco’s nationwide + cellular network. + To ensure prolonged device battery life and operational efficiency, the + Service Provider seeks to activate power-saving configurations for its IoT + fleet during periods of low activity or based on predefined thresholds. + The Service Provider’s management system invokes the IoT Network + Optimization API to dynamically adjust network connectivity parameters. + This includes optimizing data transmission intervals, reducing signal + strength during idle phases, and scheduling sleep cycles for devices + without disrupting critical service functionality. The API evaluates + network conditions, device locations, and application requirements to apply + energy-efficient settings while maintaining guaranteed quality-of-service + levels. By leveraging the API, the Provider ensures IoT devices consume + minimal power during operation, significantly extending battery lifetimes + and reducing energy costs. The optimization accounts for both device-level + energy savings and reduced overhead on the Telco’s network infrastructure + (e.g., lower RAN utilization during sleep cycles). Clients benefit from + uninterrupted service with no manual + intervention, aligning sustainability goals with operational reliability.\ + \ + **Example use case and flow:**\ + \ + [**Service**](https://github.com/camaraproject/\ + IoTNetworkOptimization/blob/main/documentation/API_documentation/\ + IoT_Network_Optimization_UserStory_UseCase_1.md)\ + \ + **The main elements of the IoT Network Optimization API are:**\ + \ + **PowerSavingRequest:** + Provides to the API Producer the intention of a enabling or disabling power + saving features for a specific set of IoT devices.\ + \ + **PowerSavingResponse:** + Provides to the API Consumer the status of the power-saving feature + activation based on the related transaction.\ + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details on how + an API consumer requests an access token. Please refer to Identify and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile.\ + \ + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API + provider, taking into account the declared purpose for accessing the API, + whilst also being subject to the prevailing legal framework dictated by + local legislation.\ + \ + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + ## API Documentation + ## Details + The IoT Network Optimization API provides the API Consumer with the + capability to activate and manage IoT-specific network features for a fleet + of connected devices. The API enables optimized power consumption + transmission by leveraging network-level configurations tailored for IoT + deployments. + + The IoT API allows an IoT Service Provider to dynamically adjust network + parameters to optimize device performance and reduce operational overhead. + The IoT API Consumer (typically the IoT Service Provider or a third-party + management system) invokes the API with identifiers for the target IoT + devices. The API then applies the requested optimizations, such as enabling + low-power modes for battery-operated sensors. + + By using the IoT Network Optimization API, Service Providers can ensure + their IoT deployments operate at peak efficiency extending device battery + life and improving overall service reliability. + + The IoT Network Optimization API is an intent based API. + \ + The IoT Network Optimization API supports the following Intent: + - Intent1: I would like to activate power-saving features for my IoT + devices during a specified period. + + The inputs for the above intent are: + - IoT devices (e.g., device identifiers like IPs or SIM phone number) + - power-saving desired status + - time frame (e.g., start/end timestamps) + + The output for the above intent are: + - activation status (success/failure per device or group) + - transaction ID for tracking + + The related endpoint is: + - Intent: /features/power-saving + + ## Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guidelines`. + + Please refer to [CAMARA_common.yaml]({link_to_release}/CAMARA_common.yaml) + for a complete list of error responses. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + ## FAQ's + (FAQs will be added in a later version of the documentation) + ## Release Notes + First draft for the IoT Network Optimization API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.5 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/IoTNetworkOptimization +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/iot-network-optimization/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root for the IoT Network Optimization API +security: + - notificationsBearerAuth: [] +tags: + - name: Power Saving + description: Enable/Disable power-saving features. +############################################################################ +# Paths # +############################################################################ +paths: + /features/power-saving: + post: + tags: + - Power Saving + summary: Activate or de-activate power-saving features for IoT devices + operationId: activatePowerSaving + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - oAuth2: + - 'iot-management:power-saving:write' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingRequest' + responses: + "202": + description: Power-saving feature request accepted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingResponse' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/Generic409" + "501": + $ref: "#/components/responses/Generic501" + callbacks: + onTransactionCompleted: + $ref: "#/components/callbacks/onTransactionCompleted" + /features/power-saving/transactions/{transactionId}: + get: + parameters: + - name: transactionId + in: path + required: true + schema: + $ref: '#/components/schemas/TransactionId' + - $ref: '#/components/parameters/x-correlator' + tags: + - Power Saving + summary: Get status of a transaction for power-saving features + operationId: getPowerSaving + security: + - oAuth2: + - 'iot-management:power-saving:read' + responses: + "200": + description: Power-saving features activated successfully + content: + application/json: + schema: + $ref: '#/components/schemas/PowerSavingResponse' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "501": + $ref: "#/components/responses/Generic501" + +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + oAuth2: + type: oauth2 + description: This API uses OAuth 2 + [More info](https://api.example.com/docs/auth) + flows: + clientCredentials: + tokenUrl: 'https://example.com/oauth/token' + scopes: + 'iot-management:power-saving:read': + Grants access to read-only data in the Power Saving resources + 'iot-management:power-saving:write': + Grants write access to the Power Saving resources + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onTransactionCompleted: + # when data is sent, it will be sent to the callback url provided + "{$request.body#/subscriptionRequest/sink}": + post: + summary: Provides back the result of the enabling operations + description: | + once the system has request to enable power-settings for all + the devices it collects the results and provides it back to + the API Consumer + operationId: IoTNetworkOptimizationNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: payload containing the operation results + required: true + content: + application/cloudevents+json: + schema: + allOf: + - $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + type: "org.camaraproject.iot-network-optimization-notification.v1.power-saving" + specversion: "1.0" + datacontenttype: "application/json" + data: + activationStatus: + - device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + status: "pending" + transactionId: "string" + time: "2018-04-05T17:31:00Z" + responses: + "202": + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "204": + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + ############################################################################ + # Resources # + ############################################################################ + schemas: + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 2 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.iot-network-optimization-notification.v1.power-saving + - org.camaraproject.iot-network-optimization-notification.v1.power-saving.error + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.iot-network-optimization-notification.v1.power-saving + - org.camaraproject.iot-network-optimization-notification.v1.power-saving.error + PowerSavingRequest: + type: object + required: + - devices + - enabled + - subscriptionRequest + properties: + devices: + type: array + items: + $ref: '#/components/schemas/Device' + description: Device IDs or group identifiers + enabled: + type: boolean + timePeriod: + required: + - startDate + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. + If not included, then the period has no ending date. + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required in + CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.iot-network-optimization-notification.v1.power-saving: "#/components/schemas/CloudEventPowerSaving" + org.camaraproject.iot-network-optimization-notification.v1.power-saving.error: "#/components/schemas/CloudEventError" + CloudEventPowerSaving: + description: provides back the power saving operation result. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + $ref: "#/components/schemas/PowerSavingResponse" + + CloudEventError: + description: Error notification for a power saving report request. + allOf: + - $ref: "#/components/schemas/CloudEvent" + properties: + data: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + transactionId: + type: string + format: uuid + description: Transaction identifier allocated for enabling/disabling IoT + features + required: + - transactionId + + PowerSavingResponse: + type: object + properties: + activationStatus: + type: array + items: + $ref: '#/components/schemas/DeviceStatus' + transactionId: + type: string + + DeviceStatus: + type: object + properties: + device: + $ref: '#/components/schemas/Device' + status: + type: string + enum: [pending, in-progress, success, failed] + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device + identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the MNO might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible + across different MNOs. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In + mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to + E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile + network. In 3GPP terminology, it corresponds to the GPSI formatted with + the External Identifier ({Local Identifier}@{Domain Identifier}). + Unlike the telephone number, the network access identifier is not + subjected to portability ruling in force, and is individually managed + by each operator. + type: string + example: "123456789@domain.com" + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is not + in use) then the same address should be specified for both + publicAddress and privateAddress. + If NAT64 is in use, the device should be identified by its publicAddress + and publicPort, or separately by its allocated IPv6 address (field + ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + TransactionId: + type: string + format: uuid + description: Transaction identifier allocated for enabling/disabling IoT + features + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ############################################################################ + # Responses # + ############################################################################ + ErrorInfo: + description: error information + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: | + Request cannot be authenticated and a new authentication is + required + value: + status: 401 + code: UNAUTHENTICATED + message: | + Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - UNKNOWN_APPLICATION_IDENTIFIER + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Application Identifier unknown + value: + status: 404 + code: UNKNOWN_APPLICATION_IDENTIFIER + message: the target application is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + description: Device already in the requested state or conflicting operation in progress + value: + status: 409 + code: CONFLICT + message: The device is already in the requested power-saving state or a conflicting operation is in progress. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: the Application Identifier is not included in the + request + value: + status: 422 + code: MISSING_IDENTIFIER + message: unspecified Application Identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily + blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code + should be avoided as far as possible to get the objective + to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. diff --git a/original/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1.md b/original/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1.md new file mode 100644 index 0000000000000000000000000000000000000000..9949cd4e01d9e0d464df726f6ea82a8dee405cc5 --- /dev/null +++ b/original/IoTNetworkOptimization/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1.md @@ -0,0 +1,11 @@ + +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service Provider partners with a Telco Operator to deploy IoT devices (e.g., sensors, trackers) across the Telco’s nationwide cellular network. To ensure prolonged device battery life and operational efficiency, the Service Provider seeks to activate power-saving configurations for its IoT fleet during periods of low activity or based on predefined thresholds. The Service Provider’s management system invokes the IoT Network Optimization API to dynamically adjust network connectivity parameters. This includes optimizing data transmission intervals, reducing signal strength during idle phases, and scheduling sleep cycles for devices without disrupting critical service functionality. The API evaluates network conditions, device locations, and application requirements to apply energy-efficient settings while maintaining guaranteed quality-of-service levels. By leveraging the API, the Provider ensures IoT devices consume minimal power during operation, significantly extending battery lifetimes and reducing energy costs. The optimization accounts for both device-level energy savings and reduced overhead on the Telco’s network infrastructure (e.g., lower RAN utilization during sleep cycles). Clients benefit from uninterrupted service with no manual intervention, aligning sustainability goals with operational reliability.| M | +|Roles, Actor(s) and scope|• Service Provider: role of IoT Network Optimization API consumer
                                              API Provider: role of IoT Network Optimization API provider
                                              • Operator Platform ([EdgeCloud/documentation/SupportingDocuments/Edge terminology/edge_terminology.md at main · camaraproject/EdgeCloud](https://github.com/camaraproject/EdgeCloud/blob/main/documentation/SupportingDocuments/Edge%20terminology/edge_terminology.md)): role of Service host
                                              • End User: both Teclo Operator's subscribers and Service Provider customer, role of Service consumer
                                              • Scope: Computing Services (OGW Taxonomy)| M | +|NF Requirements|NA| O | +|Pre-conditions|• The Service Provider has a fleet of IoT devices
                                              • The IoT devices are connected to the Operator network.| M | +|Begins when|The API Consumer invokes the IoT Network Optimization API to set power-saving features for a fleet of IoT devices with a specific configuration.| M | +|Step 2|The API Provider returns a transaction identifier to check the status of the request. | M| +|Step 3|The API Provider invokes a callback to the API Consumer to notifiy the final status of the requested operation. | M | +|Post-conditions|The Service Provider devices can leverege an optimized network configuration to save power. | M | diff --git a/original/IoTNetworkOptimization/documentation/API_documentation/README.MD b/original/IoTNetworkOptimization/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTNetworkOptimization/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist.md b/original/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..e2d7139224b5ab609777e36a236551ac526e34e1 --- /dev/null +++ b/original/IoTNetworkOptimization/documentation/API_documentation/iot-network-optimization-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for iot-network-optimization v0.1.0-alpha.1 in r1.1 + +| Nr | API release assets | alpha | release-candidate | initial
                                              public | stable
                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/iot-network-optimization.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | N | not fully checked | +| 3 | Guidelines from ICM applied | O | M | M | M | N | not fully checked | +| 4 | API versioning convention applied | M | M | M | M | Y | 0.1.0-alpha.1 | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/iot-network-optimization.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/IoT_Network_Optimization_UserStory_UseCase_1) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/iot-network-optimization-power-saving.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.1 | +| 11 | Change log updated | M | M | M | M | Y | | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AQCGDg) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/IoTNetworkOptimization/documentation/SupportingDocuments/README.MD b/original/IoTNetworkOptimization/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTNetworkOptimization/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTSIMFraudPrevention/README.md b/original/IoTSIMFraudPrevention/README.md new file mode 100644 index 0000000000000000000000000000000000000000..8567e396e0f6303b3796d3ced5fc26af271e174f --- /dev/null +++ b/original/IoTSIMFraudPrevention/README.md @@ -0,0 +1,41 @@ + + + + + + + + + +# IoTSIMFraudPrevention + +Sandbox API Repository to describe, develop, document, and test the IoT SIM Fraud Prevention Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/xwKaBQ) + +## Scope + +* Service API(s) “IoTSIMFraudPrevention” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * manage device-card binding, includes bindng/unbinding imei to the card, when the imei is not match with the bind information, operator will block the network, when the imei is match, resume the network.. + * manage device-area binding, includes binding/unbinding area to the card, when the area is not match with the bind information, operator will block the network, when the area is match, resume the network. + * query risk control information related to IoT SIM cards, includes machine-card binding and region restriction. +* Describe, develop, document, and test the API(s) +* Started: March 2025 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Every 2 weeks on Wednesdays at 9:00 UTC (start from April 30th, 2025) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92159554978?password=c5c63329-3b55-4fe0-94d9-9091c51f2ef9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/GwCfBQ) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/IoTSIMFraudPrevention/code/API_definitions/README.MD b/original/IoTSIMFraudPrevention/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/IoTSIMFraudPrevention/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions.yaml b/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..db0d2bd64d748b1a3f047ab0123fba77fd6d21b7 --- /dev/null +++ b/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention-subscriptions.yaml @@ -0,0 +1,1536 @@ +openapi: 3.0.3 +info: + title: IoT SIM Fraud Prevention Subscriptions + description: | + API to subscribe to events related to SIM card binding and regional restrictions. + + # Introduction + This API allows enterprise customers to subscribe to risk control information about IoT SIM cards. + When a bound device changes IMEI or moves in/out of a restricted area, a notification is sent to the registered callback endpoint. + + # Relevant terms and definitions + * **SIM card**: IoT network card (subscriber identity module). + * **Binding**: mechanism linking a SIM card to a specific terminal device (IMEI) or area. + * **Device**: any physical entity that can connect to a network. + * **IMEI**: International Mobile Equipment Identity. + + # API Functionality + The API provides endpoints to manage subscriptions: + - `POST /subscriptions` – create a subscription. + - `GET /subscriptions/{subscriptionId}` – retrieve a subscription. + - `DELETE /subscriptions/{subscriptionId}` – delete a subscription. + + # Notifications + When a subscribed event occurs, the server sends a `POST` request to the `sink` URL provided by the subscriber. + The notification payload conforms to the CloudEvents specification. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification MAY not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.7.0 +externalDocs: + description: CAMARA API Design Guidelines + url: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design/API-design.md +servers: + - url: "{apiRoot}/iot-sim-fraud-prevention-subscriptions/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +paths: + /subscriptions: + post: + tags: + - Subscription sim card fraud prevention + summary: Subscribe to IMEI or area change events + description: | + Create a subscription to receive notifications when the IMEI of a device changes or when it enters/leaves a restricted area. + operationId: subscribeFraudPrevention + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: Subscription For One Device By IPv4 Address + description: Use the IPv4 address of a device for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_IPV6_ADDRESS: + summary: Subscription For One Device By IPV6 Address + description: Use the IPv6 address of a device for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_PHONE_NUMBER: + summary: Subscription For One Device By Device Number + description: Use a device's phone number for subscription operation + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + phoneNumber: "+123456789" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: Subscription For One Device By Network Access Identification + description: Use a device's network access identifier for subscription operations + value: + config: + subscriptionExpireTime: "2024-03-22T05:40:58.469Z" + initialEvent: true + subscriptionMaxEvents: 10 + subscriptionDetail: + device: + networkAccessIdentifier: "123456789@domain.com" + types: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + sink: "https://notificationSendServer12.supertelco.com" + protocol: "HTTP" + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9" + accessTokenExpiresUtc: "2024-03-23T05:40:58.469Z" + accessTokenType: "bearer" + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important note: This endpoint will be implemented by API users. + Whenever an IMEI or area change event occurs, the server will call this endpoint. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/NotificationEvent" + examples: + IMEI_CHANGE: + description: The trigger event when the device IMEI has changed + value: + specversion: "1.0" + source: "https://api.example.com" + id: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + type: "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + datacontenttype: "application/json" + time: "2023-03-22T05:40:23.682Z" + data: + subscriptionId: "987654321" + imei: "35-209900-176148-1" + device: + phoneNumber: "+123456789" + AREA_CHANGE: + description: The trigger event when the device area has changed + value: + specversion: "1.0" + source: "https://api.example.com" + id: "b4333c46-49c0-4f62-80d7-f0ef930f1c47" + type: "org.camaraproject.iot-sim-fraud-prevention.v0.area-change" + datacontenttype: "application/json" + time: "2023-03-22T05:41:23.682Z" + data: + subscriptionId: "987654321" + area: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 2000 + device: + phoneNumber: "+123456789" + responses: + "204": + description: Successful notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/CallbackBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "410": + $ref: "#/components/responses/Callback410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Created (Successful creation of subscription). + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: | + The result of subscription machine card binding or region restriction change events + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscribeFraudPreventionResponseAsync" + examples: + RESULT_SUBSCRIPTION_ID: + summary: subscription result + description: | + The result of subscription device's IMEI or region change + value: + subscriptionId: "1119920371" + "400": + $ref: "#/components/responses/SubscribeBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Subscribe422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:subscribe" + + get: + tags: + - Subscription management + summary: List subscriptions + description: Retrieve a list of existing subscriptions. + operationId: listSubscriptions + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: List of subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + maxItems: 1000 + items: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:read" + + /subscriptions/{subscriptionId}: + get: + tags: + - Subscription management + summary: Get subscription details + description: Retrieve the details of an existing subscription. + operationId: getSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: subscriptionId + in: path + required: true + schema: + type: string + description: Identifier of the subscription. + responses: + "200": + description: Subscription details. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:read" + + delete: + tags: + - Subscription management + summary: Delete subscription + description: Delete an existing subscription. After deletion, no further notifications will be sent. + operationId: deleteSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + - name: subscriptionId + in: path + required: true + schema: + type: string + description: Identifier of the subscription. + responses: + "204": + description: Subscription successfully deleted. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed asynchronously. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention-subscriptions:delete" + +components: + securitySchemes: + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + description: | + Bearer token authentication for the callback endpoint. The token format is determined + by `sinkCredential.credentialType` in the subscription request. + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + description: Correlation id for the request + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + + # ---------- Notification ---------- + CloudEvent: + type: object + description: | + CloudEvents 1.0 specification envelope. + This schema is the stable base for all CAMARA event notifications. + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + maxLength: 256 + description: Identifier of this event, unique within the source context. + source: + $ref: "#/components/schemas/Source" + type: + type: string + maxLength: 512 + description: | + Identifies the event type. CAMARA APIs use reverse-DNS notation: + `org.camaraproject...` + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload. Structure is defined by each concrete event schema. + time: + $ref: "#/components/schemas/DateTime" + + Source: + type: string + format: uri-reference + minLength: 1 + maxLength: 2048 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://api.example.com" + + DateTime: + type: string + format: date-time + maxLength: 64 + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + # ───────────────────────────────────────────────────────────────────────── + # API-specific notification event group + # ───────────────────────────────────────────────────────────────────────── + + ApiNotificationEvent: + description: | + API-specific notification event group. + Extends the CloudEvent envelope and constrains `type` to the set of + event types defined by this API project. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + $ref: "#/components/schemas/ApiEventType" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.iot-sim-fraud-prevention.v0.imei-change: "#/components/schemas/ImeiChangeEvent" + org.camaraproject.iot-sim-fraud-prevention.v0.area-change: "#/components/schemas/AreaChangeEvent" + + ApiEventType: + type: string + description: | + Enum of API-specific event type strings for this API project. + The reverse-DNS prefix `org.camaraproject.iot-sim-fraud-prevention` makes each value + globally unique. + enum: + - org.camaraproject.iot-sim-fraud-prevention.v0.imei-change + - org.camaraproject.iot-sim-fraud-prevention.v0.area-change + + ImeiChangeEvent: + description: Event structure for IMEI change notification + allOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/ImeiChangeEventData" + + ImeiChangeEventData: + type: object + required: + - subscriptionId + - imei + - device + properties: + subscriptionId: + type: string + description: The ID of the subscription that triggered this notification + example: "987654321" + imei: + type: string + description: The new IMEI of the device + example: "35-209900-176148-1" + device: + $ref: "#/components/schemas/Device" + + AreaChangeEvent: + description: Event structure for area change notification + allOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/AreaChangeEventData" + + AreaChangeEventData: + type: object + required: + - subscriptionId + - area + - device + properties: + subscriptionId: + type: string + description: The ID of the subscription that triggered this notification + example: "987654321" + area: + $ref: "#/components/schemas/Area" + device: + $ref: "#/components/schemas/Device" + + # ───────────────────────────────────────────────────────────────────────── + # Subscription lifecycle event group (Commonalities-owned) + # ───────────────────────────────────────────────────────────────────────── + + SubscriptionLifecycleEvent: + description: | + Subscription lifecycle event group, common to all CAMARA APIs that + support explicit subscriptions. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + $ref: "#/components/schemas/SubscriptionLifecycleEventType" + discriminator: + propertyName: type + mapping: + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.iot-sim-fraud-prevention.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + + SubscriptionLifecycleEventType: + type: string + description: | + Enum of subscription lifecycle event type strings. + enum: + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-started + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-updated + - org.camaraproject.iot-sim-fraud-prevention.v0.subscription-ended + + EventSubscriptionStarted: + description: event structure for event subscription started + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + type: string + maxLength: 512 + description: Description of subscription initiation + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + type: string + maxLength: 512 + description: Description of subscription update + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned subscription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned subscription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + type: string + maxLength: 512 + description: Description of subscription termination + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester with credential type `ACCESSTOKEN`) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + # ───────────────────────────────────────────────────────────────────────── + # Callback union (API project-owned) + # ───────────────────────────────────────────────────────────────────────── + + NotificationEvent: + description: | + Union of all valid notification event groups at the callback endpoint. + oneOf: + - $ref: "#/components/schemas/ApiNotificationEvent" + - $ref: "#/components/schemas/SubscriptionLifecycleEvent" + + # ---------- Subscription schemas ---------- + Subscription: + description: Represents an event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + - startsAt + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + maxLength: 2048 + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered. + example: "https://endpoint.example.com/sink" + types: + description: Event types eligible to be delivered. + type: array + minItems: 1 + maxItems: 1 + items: + type: string + example: + - "org.camaraproject.iot-sim-fraud-prevention.v0.imei-change" + config: + $ref: "#/components/schemas/Config" + id: + type: string + description: Unique identifier of the subscription. + example: "1119920371" + startsAt: + type: string + format: date-time + description: Date when the subscription begins. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: Date when the subscription expires (if applicable). + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: Current status of the subscription. + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionResponse" + MQTT3: "#/components/schemas/MQTTSubscriptionResponse" + MQTT5: "#/components/schemas/MQTTSubscriptionResponse" + AMQP: "#/components/schemas/AMQPSubscriptionResponse" + NATS: "#/components/schemas/NATSSubscriptionResponse" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionResponse" + + SubscriptionAsync: + description: Response for a subscription request managed asynchronously + type: object + required: + - id + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + maxLength: 256 + description: The unique identifier of the subscription + example: "1119920371" + + SubscribeFraudPreventionResponseAsync: + description: Response for an asynchronous subscription creation. + type: object + properties: + subscriptionId: + type: string + description: The unique identifier of the subscription. + example: "1119920371" + required: + - subscriptionId + + SubscribeFraudPreventionRequest: + description: Request to create a subscription. + type: object + required: + - sink + - protocol + - config + - types + properties: + config: + $ref: "#/components/schemas/Config" + types: + description: Event types to subscribe to (only one allowed per subscription). + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/ApiEventType" + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + maxLength: 2048 + pattern: ^https:\/\/.+$ + description: The callback URL where notifications will be sent. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + Config: + description: Configuration parameters for the subscription. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/SubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: "2023-01-17T13:18:23.682Z" + subscriptionMaxEvents: + type: integer + minimum: 1 + example: 5 + initialEvent: + type: boolean + + SubscriptionDetail: + description: Details specific to the subscribed events. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + required: + - device + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Delivery protocol (only HTTP is currently allowed). + example: "HTTP" + + # ---------- Sink credentials ---------- + SinkCredential: + type: object + description: Authentication/authorization information for the callback sink. + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - PRIVATE_KEY_JWT + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + PRIVATE_KEY_JWT: "#/components/schemas/PrivateKeyJWTCredential" + required: + - credentialType + + PlainCredential: + type: object + description: Plain username/password credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + type: string + secret: + type: string + + AccessTokenCredential: + type: object + description: Bearer token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + type: string + accessTokenExpiresUtc: + type: string + format: date-time + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + PrivateKeyJWTCredential: + type: object + description: Use PRIVATE_KEY_JWT to get an access token. The authorization server information needed for this type of sink credential (token endpoint, client ID, JWKS URL) is shared upfront between the client and the CAMARA entity. This type of credential is to be used by clients that have an authorization server. + allOf: + - $ref: "#/components/schemas/SinkCredential" + + # ---------- Device identification (same as main API) ---------- + Device: + description: End-user device identification. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + + # ---------- Geographic area (used in AREA_CHANGE notification) ---------- + Area: + description: Geographic area. + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + point: + $ref: "#/components/schemas/Point" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + enum: + - CIRCLE + + Circle: + description: Circular area. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + minimum: 1 + maximum: 200000 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + # ---------- Error ---------- + ErrorInfo: + description: Common error schema. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + code: + type: string + message: + type: string + + # ---------- Protocol-specific subscription schemas ---------- + HTTPSubscriptionRequest: + description: Subscription request for HTTP-based event delivery. + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + description: Subscription resource returned for HTTP-based event delivery. + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + description: HTTP protocol settings for event delivery. + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + additionalProperties: + type: string + maxLength: 512 + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + # Other protocol schemas (MQTT, AMQP, etc.) would be defined here if needed + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + maxLength: 256 + description: MQTT topic name + qos: + type: integer + format: int32 + minimum: 0 + maximum: 2 + description: Quality of Service level (0, 1, or 2) + retain: + type: boolean + expiry: + type: integer + format: int32 + minimum: 0 + maximum: 2147483647 + description: Message expiry interval in seconds + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + maxLength: 512 + linkName: + type: string + maxLength: 256 + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + maxLength: 1024 + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + maxLength: 249 + partitionKeyExtractor: + type: string + maxLength: 512 + clientId: + type: string + maxLength: 256 + ackMode: + type: integer + format: int32 + minimum: 0 + maximum: 2 + description: Acknowledgment mode (0=no ack, 1=leader ack, 2=all replicas ack) + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscribeFraudPreventionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + maxLength: 256 + description: NATS subject + required: + - subject + + # ---------- Responses ---------- + responses: + SubscribeBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_SINK + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient Types Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "SubscriptionType must be specified" + Invalid Sink Value: + value: + status: 400 + code: INVALID_SINK + message: "The sink field must be an accessible client address in order to notify the other end when an event occurs" + Invalid Protocol Value: + value: + status: 400 + code: INVALID_PROTOCOL + message: "The value of Protocol can only be HTTP, MQTT3, MQTT5, AMQP, NATS, KAFKA" + + CallbackBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + Insufficient Id Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Id must be specified" + Insufficient Type Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Type must be specified" + Insufficient Time Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Time must be specified" + Insufficient Data Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Data must be specified" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Subscribe422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + + Callback410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: + Access to the target resource is no longer available. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. diff --git a/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention.yaml b/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention.yaml new file mode 100644 index 0000000000000000000000000000000000000000..a6391eb2fe3c04669d1fc85b9c5bac4b800de9f8 --- /dev/null +++ b/original/IoTSIMFraudPrevention/code/API_definitions/iot-sim-fraud-prevention.yaml @@ -0,0 +1,1141 @@ +openapi: 3.0.3 +info: + title: IoT SIM Fraud Prevention + description: | + API for SIM card binding/unbinding and regional restriction management. + + # Introduction + This API provides operations to manage security mechanisms for IoT SIM cards: + - **Bind**: associate a SIM card with a specific device (IMEI) or restrict its operation to a geographic area. + - **Unbind**: remove an existing binding or area restriction. + - **Query**: retrieve the current binding status or area restriction for a device. + + When a device attempts to use the network, the operator checks the binding/restriction. + If the IMEI reported does not match the bound one, or the device location is outside the allowed area, + network services are automatically blocked. + + # Relevant terms and definitions + * **SIM card**: IoT network card (subscriber identity module). + * **Binding**: mechanism linking a SIM card to a specific terminal device (IMEI) to prevent misuse. + * **Device**: any physical entity that can connect to a network. + * **IMEI**: International Mobile Equipment Identity, a unique 15-digit identifier for mobile devices. + + # API Functionality + The API exposes three endpoints: + - `POST /bind` – bind IMEI or area to a card. + - `POST /unbind` – unbind IMEI or area from a card. + - `POST /query` – query binding/restriction status. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification MAY not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.7.0 +externalDocs: + description: CAMARA API Design Guidelines + url: https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design/API-design.md +servers: + - url: "{apiRoot}/iot-sim-fraud-prevention/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +paths: + /bind: + post: + tags: + - Bind sim card fraud prevention + summary: Bind device IMEI or area restrictions + description: Associate a SIM card with a specific IMEI or restrict it to a geographic area. + operationId: bindDeviceImei + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/BindDeviceImeiRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: bind imei For One Device By IPv4 Address + description: Use the IPv4 address of a device for binding operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + bindType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: bind imei For One Device By IPv6 Address + description: Use the IPv6 address of a device for binding operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + bindType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: bind imei For One Device By Phone Number + description: Use a device's number for binding operation + value: + device: + phoneNumber: "+123456789" + bindType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: bind imei For One Device By Network Access Identifier + description: Use a device's network access identifier for binding operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + bindType: "IMEIBIND" + INPUT_BIND_TYPE: + summary: bind imei For One Device By 3 Legged Token + description: Use a 3 Legged Token for binding operations (no device object needed) + value: + bindType: "IMEIBIND" + responses: + "200": + description: The result of binding the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BindDeviceImeiResponse" + examples: + BIND_SUCCESS: + summary: BOUND SUCCESSFULLY + description: The result of binding the device is successful + value: + bound: "TRUE" + BIND_FAIL: + summary: BOUND FAILED + description: The result of binding the device is a failure + value: + bound: "FALSE" + "400": + $ref: "#/components/responses/BindBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Bind422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:bind" + + /unbind: + post: + tags: + - Unbind sim card fraud prevention + summary: Unbind device IMEI or area restrictions + description: Remove an existing IMEI binding or area restriction from a device. + operationId: unBindDeviceImei + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/UnBindDeviceImeiRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: unbind imei For One Device By IPv4 Address + description: Use the IPv4 address of a device for unbinding operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + unBindType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: unbind imei For One Device By IPv6 Address + description: Use the IPv6 address of a device for unbinding operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + unBindType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: unbind imei For One Device By Phone Number + description: Use a device's number for unbinding operation + value: + device: + phoneNumber: "+123456789" + unBindType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: unbind imei For One Device By Network Access Identifier + description: Use a device's network access identifier for unbinding operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + unBindType: "IMEIBIND" + INPUT_UNBIND_TYPE: + summary: unbind imei For One Device By 3 Legged Token + description: Use a 3 Legged Token for unbinding operations (no device object needed) + value: + unBindType: "IMEIBIND" + responses: + "200": + description: The result of unbinding the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/UnBindDeviceImeiResponse" + examples: + UNBIND_SUCCESS: + summary: UNBOUND SUCCESSFULLY + description: The result of unbinding the device is successful + value: + unbound: "TRUE" + UNBIND_FAIL: + summary: UNBOUND FAILED + description: The result of unbinding the device is a failure + value: + unbound: "FALSE" + "400": + $ref: "#/components/responses/UnbindBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Unbind422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:unbind" + + /query: + post: + tags: + - Query card fraud prevention + summary: IoT SIM Fraud Prevention Query + description: Retrieve the current IMEI binding status or area restriction for a device. + operationId: query + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/QueryRequest" + examples: + INPUT_IPV4_ADDRESS: + summary: query For One Device By IPv4 Address + description: Use the IPv4 address of a device for query operations + value: + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + queryType: "IMEIBIND" + INPUT_IPV6_ADDRESS: + summary: query For One Device By IPv6 Address + description: Use the IPv6 address of a device for query operations + value: + device: + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + queryType: "IMEIBIND" + INPUT_PHONE_NUMBER: + summary: query For One Device By Phone Number + description: Use a device's number for query operation + value: + device: + phoneNumber: "+123456789" + queryType: "IMEIBIND" + INPUT_NETWORK_ACCESS_IDENTIFIER: + summary: query For One Device By Network Access Identifier + description: Use a device's network access identifier for query operations + value: + device: + networkAccessIdentifier: "123456789@domain.com" + queryType: "IMEIBIND" + INPUT_UNBIND_TYPE: + summary: query For One Device By 3 Legged Token + description: Use a 3 Legged Token for query operations (no device object needed) + value: + queryType: "IMEIBIND" + responses: + "200": + description: The result of query the device + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/QueryFraudPreventionResponse" + examples: + AREA_LIMIT_RESULT: + summary: AREALIMIT RESULT + description: The result of query sim card area limit + value: + areaLimit: + areaLimitStatus: "RESTRICTED" + limitArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + IMEI_BIND_RESULT: + summary: BINDIMEI RESULT + description: The result of query sim card imei bind + value: + imeiBind: + bindImei: "35-209900-176148-1" + bindStatus: "BOUND" + "400": + $ref: "#/components/responses/QueryBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Query422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "iot-sim-fraud-prevention:query" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.org/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + description: Correlation id for the request + example: "123e4567-e89b-12d3-a456-426614174000" + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + + # ---------- Bind / Unbind / Query common schemas ---------- + Device: + description: | + End-user device able to connect to a mobile network. + The developer can choose to provide one or more of the following identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + If multiple identifiers are provided, they MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription, formatted according to E.164 with a leading '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network (e.g., GPSI formatted as External Identifier). + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + Identification of a device using its IPv4 address. + At least one of `privateAddress` or `publicPort` must be provided together with `publicAddress`. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask. + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number. + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + A single IPv6 address identifying the device. + type: string + format: ipv6 + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + + # ---------- Bind ---------- + BindType: + type: string + description: The type of binding operation (IMEI or area limit). + enum: + - AREALIMIT + - IMEIBIND + + BindDeviceImeiRequest: + description: Request to bind IMEI or area limit to a device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + bindType: + $ref: "#/components/schemas/BindType" + required: + - bindType + + BindDeviceImeiResponse: + description: Response indicating whether the binding operation succeeded. + type: object + required: + - bound + properties: + bound: + type: string + description: "TRUE if binding succeeded, FALSE otherwise." + example: "TRUE" + + # ---------- Unbind ---------- + UnbindType: + type: string + description: The type of unbinding operation (IMEI or area limit). + enum: + - AREALIMIT + - IMEIBIND + + UnBindDeviceImeiRequest: + description: Request to unbind IMEI or area limit from a device. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + unBindType: + $ref: "#/components/schemas/UnbindType" + required: + - unBindType + + UnBindDeviceImeiResponse: + description: Response indicating whether the unbinding operation succeeded. + type: object + required: + - unbound + properties: + unbound: + type: string + description: "TRUE if unbinding succeeded, FALSE otherwise." + example: "TRUE" + + # ---------- Query ---------- + QueryType: + type: string + description: The type of query (IMEI binding or area limit). + enum: + - AREALIMIT + - IMEIBIND + + QueryRequest: + description: Request to query the current status. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + queryType: + $ref: "#/components/schemas/QueryType" + required: + - queryType + + QueryFraudPreventionResponse: + description: Response containing the requested status. + type: object + properties: + areaLimit: + $ref: "#/components/schemas/AreaLimit" + imeiBind: + $ref: "#/components/schemas/ImeiBind" + + ImeiBind: + description: IMEI binding status and bound IMEI (if any). + type: object + properties: + bindImei: + $ref: "#/components/schemas/BindImei" + bindStatus: + $ref: "#/components/schemas/BindStatus" + + BindImei: + description: The IMEI currently bound to the SIM card (15 digits). + type: string + example: "35-209900-176148-1" + + BindStatus: + description: | + Status of the IMEI binding. + - `BOUND`: an IMEI is bound. + - `UNBOUND`: no IMEI is bound. + type: string + enum: + - BOUND + - UNBOUND + + AreaLimit: + description: Area restriction status and details of the restricted area. + type: object + properties: + limitArea: + $ref: "#/components/schemas/Area" + areaLimitStatus: + $ref: "#/components/schemas/AreaLimitStatus" + + AreaLimitStatus: + description: | + Current status of area restrictions. + - `RESTRICTED`: the device is currently restricted to a specific area. + - `UNRESTRICTED`: no area restriction is active. + type: string + enum: + - RESTRICTED + - UNRESTRICTED + + # ---------- Geographic area ---------- + Area: + description: Base schema for geographic areas. + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + point: + $ref: "#/components/schemas/Point" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + + AreaType: + type: string + description: Type of the area. + enum: + - CIRCLE + + Circle: + description: A circular area defined by a center point and a radius. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: integer + description: Radius in meters (minimum 1, maximum 200000). + minimum: 1 + maximum: 200000 + required: + - center + - radius + example: + areaType: CIRCLE + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 50000 + + Point: + type: object + description: Coordinates (latitude, longitude). + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component (-90 to 90). + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + + Longitude: + description: Longitude component (-180 to 180). + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + + # ---------- Error ---------- + ErrorInfo: + description: Common error schema. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code. + code: + type: string + description: Error code. + message: + type: string + description: Human-readable explanation. + + # ---------- Responses ---------- + responses: + BindBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient BindType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "BindType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid BindType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of bindType can only be IMEIBIND,AREALIMIT" + + UnbindBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient UnbindType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "UnbindType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid UnbindType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of unbindType can only be IMEIBIND,AREALIMIT" + + QueryBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + Insufficient Device Parameters: + description: Sufficient parameters must be provided to allow the target UE to be identified + value: + status: 400 + code: INVALID_ARGUMENT + message: "At least one of phoneNumber, networkAccessIdentifier, ipv4Address and ipv6Address must be specified" + Insufficient QueryType Parameters: + value: + status: 400 + code: INVALID_ARGUMENT + message: "QueryType must be specified" + Inconsistent Device Properties: + description: Device parameters provided identify different devices + value: + status: 400 + code: INVALID_ARGUMENT + message: "Multiple inconsistent device parameters specified" + Invalid Network Access Identifier: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: networkAccessIdentifier" + Invalid Phone Number: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: phoneNumber" + Invalid IPv4 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv4Address" + Invalid IPv6 Address: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid format: ipv6Address" + Invalid Port Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "Invalid value: ipv4Address.publicPort" + Invalid QueryType Value: + value: + status: 400 + code: INVALID_ARGUMENT + message: "The value of queryType can only be IMEIBIND,AREALIMIT" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + Bind422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - UNNECESSARY_UNBIND_IMEI + - UNNECESSARY_UNBIND_AREALIMIT + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Unnecessary Unbind BINDIMEI: + description: The IMEI of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_IMEI + message: The current device imei has been unbound + Unnecessary Unbind AREALIMIT: + description: The area limit of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_AREALIMIT + message: The current device area limit has been unbound + + Unbind422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - UNNECESSARY_UNBIND_IMEI + - UNNECESSARY_UNBIND_AREALIMIT + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + Unnecessary Unbind BINDIMEI: + description: The IMEI of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_IMEI + message: The current device imei has been unbound + Unnecessary Unbind AREALIMIT: + description: The area limit of the current device has been unbound, there is no need to unbind it again + value: + status: 422 + code: UNNECESSARY_UNBIND_AREALIMIT + message: The current device area limit has been unbound + + Query422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Unsupported Identifier: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: None of the provided identifiers is supported by the implementation. + Unnecessary Identifier: + description: An explicit identifier has been provided for the device when this is already identified by the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit identifier has been provided for the device when this is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the device cannot be identified from the 2-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. diff --git a/original/IoTSIMFraudPrevention/documentation/API_documentation/README.MD b/original/IoTSIMFraudPrevention/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTSIMFraudPrevention/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md b/original/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..d63c670c4b6fe015a46d7410f74da285e259ea6d --- /dev/null +++ b/original/IoTSIMFraudPrevention/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md @@ -0,0 +1,10 @@ +# IoT SIM Fraud Prevention API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise customer managing IoT devices, I need to prevent SIM card fraud by binding SIM cards to specific devices (IMEI binding) and restricting their usage to specific geographic areas (area restrictions). This helps me ensure that my IoT SIM cards are only used on authorized devices in authorized locations, preventing unauthorized usage and potential fraud. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:Administrator, Customer:User
                                              **Actors:** Enterprise IoT administrators, IoT platform operators, security teams. The API handles both two-legged and three-legged access tokens for device identification.
                                              **Scope:**
                                              • Bind and unbind IMEI numbers to SIM cards
                                              • Set and remove geographic area restrictions
                                              • Query current binding and restriction status
                                              • Subscribe to notifications for IMEI or area changes
                                              • Receive real-time alerts when unauthorized changes occur
                                              | +| ***Pre-conditions*** |The preconditions are listed below:
                                              1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                              2. The Customer:BusinessManager has successfully subscribed to the IoT SIM Fraud Prevention product from the product catalog.
                                              3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                              4. The Customer:User has obtained valid identifiers for the target IoT devices or will use three-legged access tokens for device identification.
                                              5. The enterprise has legitimate business needs for device binding and area restrictions for their IoT deployments.
                                              6. | +| ***Activities/Steps*** | **Starts when:**
                                                1. The customer identifies IoT devices that require fraud prevention measures

                                                **Main Operations:**
                                                2. The customer makes a POST request to `/bind` to establish IMEI binding or area restrictions for specific devices
                                                3. The customer makes a POST request to `/unbind` to remove existing bindings or restrictions when devices are decommissioned or relocated
                                                4. The customer makes a POST request to `/query` to check current binding and restriction status
                                                5. The customer makes a POST request to `/subscribe` to receive notifications when IMEI or area changes occur
                                                6. The system automatically blocks network services when unauthorized IMEI usage or area violations are detected

                                                **Ends when:**
                                                The IoT SIM cards are properly secured with appropriate bindings and restrictions, and the customer has visibility into the security status through queries and notifications. | +| ***Post-conditions*** | 1. For successful bind operations: The SIM card is bound to the specified IMEI or area, and network services will be blocked if unauthorized usage is detected.
                                                2. For successful unbind operations: The existing binding or restriction is removed, allowing the SIM card to be used on different devices or in different areas.
                                                3. For query operations: The current binding and restriction status is returned, providing visibility into the security configuration.
                                                4. For subscription operations: Notifications are sent to the specified callback URL when relevant changes occur.
                                                5. The system automatically enforces the configured security policies by blocking unauthorized usage.| +| ***Exceptions*** | Several exceptions might occur
                                                - Authentication failures: Invalid, missing, or expired access tokens
                                                - Authorization failures: Insufficient permissions or scope
                                                - Invalid inputs: Missing required parameters, invalid parameter values, or inconsistent device identifiers
                                                - Device not found: Provided device identifiers don't match any known devices
                                                - Unsupported operations: Attempting to unbind when no binding exists, or using unsupported identifier types
                                                - Rate limiting: Exceeding API quota or request rate limits
                                                - Network errors: Temporary service unavailability or callback endpoint issues| \ No newline at end of file diff --git a/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist.md b/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..3d4c5e13b02e6b6887f96c3a2598d9246fbd8ef4 --- /dev/null +++ b/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for api-name api-version in rx.y. + +| Nr | API release assets | alpha | release-candidate | initial
                                                public | stable
                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](/code/API_definitions) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [relative link](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [relative link](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml (or [relative link](/documentation/API_documentation)) | +| 6 | User stories | O | O | O | M | Y | [relative link](/documentation/API_documentation/iot-sim-fraud-prevention-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/iot-sim-fraud-prevention-callback.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [relative link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | issue link | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | see (1) | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/93979335/IoTSIMFraudPrevention) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: 1. Certified companies can be found on the GSMA Open Gateway Portal: https://open-gateway.gsma.com/ + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/README.MD b/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/IoTSIMFraudPrevention/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomer/README.md b/original/KnowYourCustomer/README.md new file mode 100644 index 0000000000000000000000000000000000000000..0f554e437e5df573e23ae6d4d880e3561d7431fa --- /dev/null +++ b/original/KnowYourCustomer/README.md @@ -0,0 +1,55 @@ + + + + + + + + + +# KnowYourCustomer + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomer Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) + +* API wiki page: [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/BjPe) + + +> [!WARNING] +> After the CAMARA Spring25 meta release this repository has been separated into 3 individual repositories: +> - [KnowYourCustomerMatch](https://github.com/camaraproject/KnowYourCustomerMatch) +> - [KnowYourCustomerFill-in](https://github.com/camaraproject/KnowYourCustomerFill-in) +> - [KnowYourCustomerAgeVerification](https://github.com/camaraproject/KnowYourCustomerAgeVerification) +> +> This repository should be only used for maintenance of previous releases. For contributions to the API development please use exclusively the new repositories. Thanks! + + +## Scope + +* Service APIs for “KnowYourCustomer” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * compare the information it (Service Provider, SP) has for a particular user with that on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. (KYC Match) + * request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. (KYC Fill-in) + * check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc. (KYC Age Verification) +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: September 2023 +* Incubating stage since: February 2025 + +## Release Information + +* Note: Please be aware that the project will have updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. For best results, use the latest available release + +* `NEW`:**The latest public release of CAMARA Know Your Customer is [r2.2](https://github.com/camaraproject/KnowYourCustomer/tree/r2.2)**. The Release Tag is [r2.2](https://github.com/camaraproject/KnowYourCustomer/releases/tag/r2.2). + - Contains the following API definitions **with inline documentation**: + - kyc-match: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-match.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-match.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-match.yaml&nocors) + - kyc-fill-in: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-fill-in.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-fill-in.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-fill-in.yaml&nocors) + - kyc-age-verification: [YAML spec file](https://github.com/camaraproject/KnowYourCustomer/blob/r2.2/code/API_definitions/kyc-age-verification.yaml) | [View it on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-age-verification.yaml&nocors) | [View it on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomer/r2.2/code/API_definitions/kyc-age-verification.yaml&nocors) + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly, Tuesday, 09:00 CEST (07:00 UTC) (till October 27th 2024) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-kyc + * A message to the community of this Sub Project can be sent using diff --git a/original/KnowYourCustomer/code/API_definitions/kyc-age-verification.yaml b/original/KnowYourCustomer/code/API_definitions/kyc-age-verification.yaml new file mode 100644 index 0000000000000000000000000000000000000000..9081b0ae8d651c77ed208b872fd34f79d9a01df1 --- /dev/null +++ b/original/KnowYourCustomer/code/API_definitions/kyc-age-verification.yaml @@ -0,0 +1,507 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Age Verification + + description: | + + # Summary + This API provides the customer with the ability to check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. + + # API functionality + + The API defines one service endpoint: + + - `POST /verify` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and checks if the age of the subscriber is older than the age threshold in the request. + Additionally, as optional function, provides (1) if age check is done against another form of official identification or not (verifiedStatus), (2) an overall score of how certain is the response using both information provided in the request and information that the Operator holds(identityMatchScore), (3) an indicator on whether the subscription has any kind of content lock (contentLock) and (4) an indicator on whether the subscription has any kind of parental control activated (parentalControl). + + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). [Required only in case a 2-legged flow has been agreed between API Provider and API Consumer following CAMARA directives; otherwise, phoneNumber must not be included] + - `ageThreshold`: The age threshold from which the age of the user must be compared. [Required] + - any of `idDocument`, `name`, `givenName`, `familyName`, `middleNames`, `familyNameAtBirth`, `birthdate`, `email`; additional subscriber's information to be checked in order to confirm that the subscriber is the contract's owner [Optional] + - `includeContentLock` and `includeParentalControl`: These two flags allow the API Client to indicate that the corresponding response properties `contentLock` and `parentalControl` should be returned. Its implementation is optional for the API Provider, so in such cases, these parameters will be ignored. [Optional] + + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `ageCheck`: Indicate 'true' when the age of the user is the same age or older than the age threshold (age >= age threshold), and 'false' if not (age < age threshold). Otherwise, 'not_available'. + - `verifiedStatus`: true if the information provided was checked against another form of official identification, otherwise false. + - `identityMatchScore`: The overall score of identity information available in the Operator, information either provided in the request body comparing it to the one that the MNO holds or directly using internal MNO's information. It is optional for the Operator to return the Identity match score. + - `contentLock`: Indicates if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked). + - `parentalControl`: Indicates if the subscription associated with the phone number has any kind of parental control activated. + + ## Errors + + - If the authentication access token is not valid, a `401 UNAUTHENTICATED` error is returned + - If the API call contains a formatting or other any other syntactic error, a `400 INVALID_ARGUMENT` error is returned. + - If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API consumer has a valid access token that does not have the required scope to obtain Age Verification information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + - Other errors may be returned as specified below. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: 0.1.0 + x-camara-commonalities: 0.5 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +servers: + - url: "{apiRoot}/kyc-age-verification/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Age Verification + description: Operations to verify the age of a user. + +paths: + /verify: + post: + tags: + - Age Verification + summary: Verify Age Threshold + description: | + Verify that the age of the subscriber associated with a phone number is equal to or greater than the specified age threshold value. + + As it is possible that the person holding the contract and the end-user of the subscription may not be the same, the endpoint also admits a list of optional properties to be included in the request to improve the identification. The response may optionally include the `identityMatchScore` property with a value that indicates how certain it is that the information returned relates to the person that the API Client is requesting. To increase the reliability of the information returned, the API Provider may include in the response the `verifiedStatus` property, indicating whether the identity information in its possession has been verified against an identification document legally accepted as an age verification document. + + If the API Client indicates request properties `includeContentLock` or `includeParentalControl` with value `true` and the API Provider implements this functionality, then the response will also include `contentLock` and `parentalControl` properties to indicate if the subscription has any kind of content filtering enabled. On the other hand, if the request properties are not included or the API Client specifies value `false`, then the response properties will not be returned. If the API Provider doesn't implement this functionality, request properties will be ignored and response properties won't be returned in any case. + operationId: verifyAge + security: + - openId: + - kyc-age-verification:verify + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyRequestBody' + examples: + Two-Legged Access Token Example: + value: + ageThreshold: 18 + phoneNumber: '+34629255833' # Note: Only required in case a 2-legged flow has been agreed between API Provider and API Consumer; otherwise, do not include phoneNumber + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@example.com" + includeContentLock: true + includeParentalControl: true + Three-Legged Access Token Example: + value: + ageThreshold: 18 + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@gmail.com" + includeContentLock: true + includeParentalControl: true + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyResponseBody' + examples: + KYC_200Example: + value: + ageCheck: "true" + verifiedStatus: true + identityMatchScore: 90 + contentLock: "false" + parentalControl: "true" + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + VerifyRequestBody: + type: "object" + description: Request to verify the age threshold provided. + required: + - ageThreshold + properties: + ageThreshold: + $ref: "#/components/schemas/AgeThreshold" + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + idDocument: + $ref: "#/components/schemas/IdDocument" + name: + $ref: "#/components/schemas/Name" + givenName: + $ref: "#/components/schemas/GivenName" + familyName: + $ref: "#/components/schemas/FamilyName" + middleNames: + $ref: "#/components/schemas/MiddleNames" + familyNameAtBirth: + $ref: "#/components/schemas/FamilyNameAtBirth" + birthdate: + $ref: "#/components/schemas/Birthdate" + email: + $ref: "#/components/schemas/Email" + includeContentLock: + $ref: "#/components/schemas/IncludeContentLock" + includeParentalControl: + $ref: "#/components/schemas/IncludeParentalControl" + + AgeThreshold: + type: "integer" + minimum: 0 + maximum: 120 + description: The age to be verified. The indicated range is a global definition of maximum and minimum values allowed to be requested. It is important to note that this range might be more restrictive in some implementations due to local regulations of a country i.e. A country does not allow to request for an age under 18. This limitation must be informed during the onboarding process. + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + IdDocument: + type: "string" + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + Name: + type: "string" + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + GivenName: + type: "string" + description: First/given name or compound first/given name of the customer. + + FamilyName: + type: "string" + description: Last name, family name, or surname of the customer. + + MiddleNames: + type: "string" + description: Middle name/s of the customer. + + FamilyNameAtBirth: + type: "string" + description: Last/family/sur- name at birth of the customer. + + Birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + Email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + IncludeContentLock: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `contentLock` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + IncludeParentalControl: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `parentalControl` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + VerifyResponseBody: + type: "object" + description: Response to an age verification request + required: + - ageCheck + properties: + ageCheck: + $ref: "#/components/schemas/AgeCheck" + verifiedStatus: + $ref: "#/components/schemas/VerifiedStatus" + identityMatchScore: + $ref: "#/components/schemas/IdentityMatchScore" + contentLock: + $ref: "#/components/schemas/ContentLock" + parentalControl: + $ref: "#/components/schemas/ParentalControl" + + AgeCheck: + type: "string" + description: Indicate `"true"` when the age of the user is the same age or older than the age threshold (age >= age threshold), and `"false"` if not (age < age threshold). If the API Provider doesn't have enough information to perform the validation, a `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + VerifiedStatus: + type: "boolean" + description: Indicate `true` if the information provided has been compared against information based on an identification document legally accepted as an age verification document, otherwise indicate `false`. + + IdentityMatchScore: + type: "integer" + minimum: 0 + maximum: 100 + description: The overall score of identity information available in the API Provider, information either provided in the request body comparing it to the one that the API Provider holds or directly using internal API Provider's information. It is optional for the API Provider to return the Identity match score. + + ContentLock: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked) and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ParentalControl: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of parental control activated and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ErrorInfo: + type: "object" + required: + - status + - code + - message + properties: + status: + type: "integer" + description: HTTP response status code + code: + type: "string" + description: Code given to this error + message: + type: "string" + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token diff --git a/original/KnowYourCustomer/code/API_definitions/kyc-fill-in.yaml b/original/KnowYourCustomer/code/API_definitions/kyc-fill-in.yaml new file mode 100644 index 0000000000000000000000000000000000000000..771c6d36a3854809f7dfd1ce51ba77b828d1ae9c --- /dev/null +++ b/original/KnowYourCustomer/code/API_definitions/kyc-fill-in.yaml @@ -0,0 +1,497 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Fill-in + + description: | + + This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + ## API Functionality + + This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + + * To fill-in the user personal data during the digital registration of an account to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + + * The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + + * For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + ### Special Scopes + + This API uses the following special scope kyc-fill-in:set-all which means that the API provider returns an API response as if all these scopes were specified in the scope value in the request: + `kyc-fill-in:phoneNumber kyc-fill-in:idDocument kyc-fill-in:name kyc-fill-in:givenName kyc-fill-in:familyName kyc-fill-in:nameKanaHankaku kyc-fill-in:nameKanaZenkaku kyc-fill-in:middleNames kyc-fill-in:familyNameAtBirth kyc-fill-in:address kyc-fill-in:streetName kyc-fill-in:streetNumber kyc-fill-in:postalCode kyc-fill-in:region kyc-fill-in:locality kyc-fill-in:country kyc-fill-in:houseNumberExtension kyc-fill-in:birthdate kyc-fill-in:email kyc-fill-in:gender` + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to request information related to an end user against the account data bound to their phone number. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + version: 0.3.0 + x-camara-commonalities: 0.5 + + +servers: + - url: '{apiRoot}/kyc-fill-in/v0.3' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Fill-in + description: Operations to provide information related to a customer identity stored the account data bound to the customer's phone number. + +paths: + /fill-in: + post: + tags: + - Fill-in + summary: Providing information related to a customer identity stored the account data bound to the customer's phone number. + + operationId: KYC_Fill-in + + security: + - openId: + - kyc-fill-in:set-all + - openId: + - kyc-fill-in:phoneNumber + - openId: + - kyc-fill-in:idDocument + - openId: + - kyc-fill-in:name + - openId: + - kyc-fill-in:givenName + - openId: + - kyc-fill-in:familyName + - openId: + - kyc-fill-in:nameKanaHankaku + - openId: + - kyc-fill-in:nameKanaZenkaku + - openId: + - kyc-fill-in:middleNames + - openId: + - kyc-fill-in:familyNameAtBirth + - openId: + - kyc-fill-in:address + - openId: + - kyc-fill-in:streetName + - openId: + - kyc-fill-in:streetNumber + - openId: + - kyc-fill-in:postalCode + - openId: + - kyc-fill-in:region + - openId: + - kyc-fill-in:locality + - openId: + - kyc-fill-in:country + - openId: + - kyc-fill-in:houseNumberExtension + - openId: + - kyc-fill-in:birthdate + - openId: + - kyc-fill-in:email + - openId: + - kyc-fill-in:gender + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_FillinRequest' + examples: + KYC_FillInBodyExample: + value: + { "phoneNumber": "+34629255833" } + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + + content: + application/json: + schema: + $ref: '#/components/schemas/KYC_FillinResponse' + examples: + KYC_Fillin200Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: 4 + postalCode: 1028460 + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: 36 + birthdate: '1978-08-22' + email: abc@example.com + gender: male + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + KYC_FillinRequest: + type: object + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + KYC_FillinResponse: + type: object + properties: + + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the id_document of the customer stored on the Operator's system. + + name: + type: string + description: Complete name of the customer stored on the Operator's system. It is usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer on the Operator's system. + + familyName: + type: string + description: Last name, family name, or surname of the customer stored on the Operator's system. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + middleNames: + type: string + description: Middle name/s of the customer stored on the Operator's system. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer stored on the Operator's system. + + address: + type: string + description: Complete address of the customer stored on the Operator's system. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address on the Operator's system. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address on the Operator's system. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: The postal code or Zip code of the customer's address, stored on the Operator's system. + + region: + type: string + description: Region/prefecture of the customer's address, stored on the Operator's system. + + locality: + type: string + description: Locality of the customer's address, stored on the Operator's system. + + country: + type: string + description: Country of the customer's address stored on the Operator's system. Format ISO 3166-1 alpha-2. + + houseNumberExtension: + type: string + description: House number extension of the customer stored on the Operator's system. Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: Birthdate of the customer, in ISO 8601 calendar date format (YYYY-MM-DD), stored on the Operator's system. + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain), stored on the Operator's system. + + gender: + type: string + description: Gender of the customer stored on the Operator's system (male/female/other). + enum: + - MALE + - FEMALE + - OTHER + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token diff --git a/original/KnowYourCustomer/code/API_definitions/kyc-match.yaml b/original/KnowYourCustomer/code/API_definitions/kyc-match.yaml new file mode 100644 index 0000000000000000000000000000000000000000..44cd5f6bc1d9ae308139c1193079ff0962a6998f --- /dev/null +++ b/original/KnowYourCustomer/code/API_definitions/kyc-match.yaml @@ -0,0 +1,642 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Match + + description: | + + This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + * **Match Score**: a numerical value that quantifies the similarity between two pieces of text based on the words they contain. This score is often used in various applications like text comparison, plagiarism detection, information retrieval, and natural language processing. The score typically reflects how well the words in one text match the words in another text. In the context of this API, this score will be used to determine how much does the input information looks like the information stored in the Operator's system. Unless otherwise captured in the implementation notes which Operators may publish, score will use the Jaro-Winkler distance algorithm for all countries. This parameter, as optional, will be returned depending on the capability of the Operator to calculate the scoring value. This means that not all Operators will implement this functionality or won't have the requested parameter available. It can happen that an Operator implements the score functionality but, for whatever reason, is not able to calculate it based on the client's input or the related stored information. For these cases, the score property related won't be returned in the response. + The range of score values is between "0" and "100", where higher scores indicate a higher similarity between the two compared parameters. + + ## API Functionality + + This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + + * To verify the user personal data during the digital registration of an account to a 3rd party service. + + * To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + + The API supports a multi-level hierarchy of property validation. In addition to the initial verification of the `phoneNumber`, an additional `idDocument` validation may occur based on different Operator requirements. This means that, in those cases, if the value of `idDocument` is not provided or it does not match the one bound to the specific phone number in the Operator systems, the operation will return an error. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the account data bound to their phone number. + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.3.0 + + x-camara-commonalities: 0.5 + +servers: + - url: '{apiRoot}/kyc-match/v0.3' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Match + description: Operations to match a customer identity against the account data bound to their phone number. + +paths: + /match: + post: + tags: + - Match + summary: Matching a customer identity by checking a set of attributes related against the account data bound to their phone number. + description: |- + Verify matching of a number of attributes related to a customer identity against the verified data bound to their phone number in the Operator systems. Regardless of whether the `phoneNumber` is explicitly stated in the request body, at least one of the other fields must be provided, otherwise a `HTTP 400 - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION` error will be returned. + + In order to proceed with the match check, some Operators may have the requirement to perform an additional level of validation based on the `idDocument` property. This means that, in those cases, the `idDocument` is required and the provided value needs to match the one stored in the Operator system associated with the indicated `phoneNumber`. This validation will be done before proceeding with the match check of the rest of the properties. The following two rules apply only in the cases where the Operator have the requirement to validate the `idDocument`: + - If no `idDocument` is provided, then a `HTTP 403 - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED` error will be returned. + - If the provided `idDocument` does not match the one stored in the Operator systems, then a `HTTP 403 - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH` error will be returned. + + The API will return the result of the matching process for each requested attribute. This means that the response will **only** contain the attributes for which validation has been requested. Possible values are: + - **true**: the attribute provided matches with the one in the Operator systems. + - **false**: the attribute provided does not match with the one in the Operator systems. + - **not_available**: the attribute is not available to validate. + operationId: KYC_Match + + security: + - openId: + - kyc-match:match + + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchRequestBody' + examples: + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + Three-Legged Without Phone Number Example: + value: + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchResponse' + examples: + KYC_Match200Example: + value: + idDocumentMatch: 'true' + nameMatch: 'true' + givenNameMatch: 'not_available' + familyNameMatch: 'not_available' + nameKanaHankakuMatch: 'true' + nameKanaZenkakuMatch: 'false' + middleNamesMatch: 'true' + familyNameAtBirthMatch: 'false' + familyNameAtBirthMatchScore: 90 + addressMatch: 'true' + streetNameMatch: 'true' + streetNumberMatch: 'true' + postalCodeMatch: 'true' + regionMatch: 'true' + localityMatch: 'not_available' + countryMatch: 'true' + houseNumberExtensionMatch: 'not_available' + birthdateMatch: 'false' + emailMatch: 'false' + emailMatchScore: 87 + genderMatch: 'false' + + '400': + $ref: '#/components/responses/Generic400' + + '401': + $ref: '#/components/responses/Generic401' + + '403': + $ref: '#/components/responses/Generic403' + + '404': + $ref: '#/components/responses/Generic404' + + '422': + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + schemas: + KYC_MatchRequestBody: + type: object + description: Payload to validate the customer data. + + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + name: + type: string + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer. + + familyName: + type: string + description: Last name, family name, or surname of the customer. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan. + + middleNames: + type: string + description: Middle name/s of the customer. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer. + + address: + type: string + description: Complete address of the customer. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: Zip code or postal code + + region: + type: string + description: Region/prefecture of the customer's address + + locality: + type: string + description: Locality of the customer's address + + country: + type: string + description: Country of the customer's address. Format ISO 3166-1 alpha-2 + + houseNumberExtension: + type: string + description: Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + gender: + type: string + description: Gender of the customer (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + MatchResult: + type: string + enum: + - 'true' + - 'false' + - 'not_available' + + MatchScoreResult: + type: integer + description: Indicates the similarity score assigned to the input value when it does not exactly match the value stored in the operator's system. This property shall only be returned when the value of the corresponding match field is `false`. + minimum: 0 + maximum: 100 + + KYC_MatchResponse: + type: object + properties: + idDocumentMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether Id number associated to the ID document of the customer matches with the one on the Operator's system. + nameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the complete name of the customer matches with the one on the Operator's system. + nameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + givenNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether First name/given name of the customer matches with the one on the Operator's system. + givenNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether last name/ family name/ surname of the customer matches with the one on the Operator's system. + familyNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaHankakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Hankaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaHankakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaZenkakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Zenkaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaZenkakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + middleNamesMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the middle names of the customer matches with the one on the Operator's system. + middleNamesMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameAtBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the Family Name At Birth of the customer matches with the one on the Operator's system. + familyNameAtBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + addressMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete address of the customer matches with the one on the Operator's system. + addressMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street name of the customer matches with the one on the Operator's system. + streetNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNumberMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street number of the customer matches with the one on the Operator's system. + streetNumberMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + postalCodeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the postal code / zip code of the customer matches with the one on the Operator's system. + regionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the region of the customer's address matches with the one on the Operator's system. + regionMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + localityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the locality of the customer's address matches with the one on the Operator's system. + localityMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country of the customer's address matches with the one on the Operator's system. + houseNumberExtensionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the house number extension of the customer's address with the one on the Operator's system. + birthdateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the birthdate of the customer matches with the one on the Operator's system. + emailMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the email address of the customer matches with the one on the Operator's system. + emailMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + genderMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the gender of the customer matches with the one on the Operator's system. + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION: + description: Indicated param combination is invalid + value: + status: 400 + code: KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + message: Indicated parameter combination is invalid + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED + - KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED: + description: The idDocument is required by the implementation + value: + status: 403 + code: KNOW_YOUR_CUSTOMER.ID_DOCUMENT_REQUIRED + message: The idDocument is required to perform the properties validation + KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH: + description: idDocument mismatch + value: + status: 403 + code: KNOW_YOUR_CUSTOMER.ID_DOCUMENT_MISMATCH + message: The idDocument needs to match the one associated with the provided phoneNumber + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided diff --git a/original/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in.md b/original/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in.md new file mode 100644 index 0000000000000000000000000000000000000000..057d82b1f21a5bc0ecb72e51325139a83c113325 --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/KYC-Fill-in.md @@ -0,0 +1,40 @@ +# CAMARA KnowYourCustomer KYC Fill-in API + +(NOTE: This API description is supposed to be incorporated into the YAML definition file in the future releases.) + +This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + +## Relevant Definitions and concepts + +* **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + +## API Functionality + +This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + +* To fill-in the user personal data during the digital registration of an account to a 3rd party service. + +The following figure is the generic high-level flows of this API. + +KYC_Fill-in_flow + +Note: + +* Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + +* When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + +* The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + +* For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + +## Resources and Operations overview + +The API provides the following endpoint: + +* An endpoint to request information related to an end user against the acount data bound to their phone number. + + diff --git a/original/KnowYourCustomer/documentation/API_documentation/KYC-Match.md b/original/KnowYourCustomer/documentation/API_documentation/KYC-Match.md new file mode 100644 index 0000000000000000000000000000000000000000..339e976b4e63f9babeb4333ca2b168c1b6612d20 --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/KYC-Match.md @@ -0,0 +1,35 @@ +# CAMARA KnowYourCustomer KYC Match API + +(NOTE: This API description is supposed to be incorporated into the YAML definition file in a future release.) + +This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + +## Relevant Definitions and concepts + +* **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + +## API Functionality + +This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + +* To verify the user personal data during the digital registration of an account to a 3rd party service. + +* To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + +The following figure is the generic high-level flows of this API. + +KYC_Match_flow + +Note: + +* Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + +* When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + +## Resources and Operations overview + +The API provides the following endpoint: + +* An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the acount data bound to their phone number. + + diff --git a/original/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story.md b/original/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..158abcbb16059c1c98cf16dbadb13873ee5afc02 --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/KnowYourCustomer_User_Story.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
                                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                1. The Customer:User has provided mandatory information of their identity
                                                2. Application developer has onboarded to MNO API
                                                3. Application developer has API credentials
                                                4. Privacy legal base requirement has been solved (Customer privacy)
                                                | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
                                                **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
                                                | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
                                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                • Not Found: The number provided is not managed by the MNO
                                                • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                | + +

                                                + +**User Story: KYC Fill-In - Get identity information of customer** +
                                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                1. The Customer:User has provided mandatory information of their identity
                                                2. Application developer has onboarded to MNO API
                                                3. Application developer has API credentials
                                                4. Privacy legal base requirement has been solved (Customer privacy)
                                                | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
                                                **Ends when:** The MNO service returns the identity information stored in its customer database.
                                                | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
                                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                • Not Found: The number provided is not managed by the MNO
                                                • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                | + + diff --git a/original/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md b/original/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..28a5471d57512cbadb9720c3d0e842220cc3ed1d --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-age-verification 0.1.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                public | stable
                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-age-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-age-verification.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/original/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md b/original/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..d3006ab6a0bce465d097793ba0d9374ef07164fa --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-fill-in 0.3.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                public | stable
                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-fill-in.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-fill-in.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md b/original/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..68d9020f3f585b39af2ba37ad274a3664ccc7859 --- /dev/null +++ b/original/KnowYourCustomer/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md @@ -0,0 +1,28 @@ +# API Readiness Checklist + +Checklist for kyc-match 0.3.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                public | stable
                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-match.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/Commonalities/releases/tag/r2.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r2.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r2.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-match.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31.md new file mode 100644 index 0000000000000000000000000000000000000000..dc39d62d5c2aac49ac447e95c168064add1c30f2 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-10-31.md @@ -0,0 +1,92 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-10-31 + +*Tuesday, October 31st, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Ludovic Robert, Orange +* Efthymios Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Surajj Jaggernath, Vodacom + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Introduction +* Proposed timeline and how to proceed +* Proposed Meeting Schedule +* Initial Codeowners +* Scope Proposal +* User Story – initial proposal +* AOB + +The Agenda was approved. + +## Introduction + +* As it was the first meeting, attendees introduced themselves to know each other. + +## Proposed timeline and how to proceed + +* Toshi showed Milestone Reference, which was GSMA (Open Gateway Product Workstream) created based on CAMARA subproject activity, with proposed timeline of each milestone including Milestone 10 stable YAML publication targeted on December 8th. +* The proposed timeline was agreed after the following clarification: + * Stable YAML publication is for both of KYC-Match and KYC-Fill-in with version 0.1 (or 0.x if applicable, but not 1.0). + * Dates of Milestone 4 & 5 was wrong and to be corrected (Oct -> Nov) [AP01], though their Week Numbers were correct. +* Toshi proposed to proceed with KYC-Match and KYC-Fill-in work in alignment with GSMA Milestone Reference, i.e. Scope & User Story -> Flow & Parameters -> YAML & Documents, as much as possible, and it was agreed. + +### Proposed Meeting Schedule + +* Toshi proposed regular meeting schedule and after discussion, it was agreed that **Bi-weekly meetings are held on Tuesday, 0900-1000 CET**. +* Note: + * 0830-0930 CET was first agreed, and then in AOB, it was changed 0900-1000 CET by Stefano’s request + * Weekly or Bi-weekly was discussed, and Members agreed with Bi-weekly as most of other CAMARA subprojects do. It is because work/discussion is supposed to be progressed on GitHub Issue/PR mostly and meetings are used for resolving issues which require real-time verbal discussion. + * However, ad-hoc meetings may be held on Tuesdays between Bi-weekly regular meetings, if needed. Meeting time for ad-hoc meetings will be decided considering any conflict with other meetings especially DeviceLocation. + * December 26th and January 2nd are to be discussed +* Meeting link for the regular meetings will be distributed by ML, and information on the regular meetings will be incorporated into GitHub KnowYourCustomer page. [AI02] + +## Initial Codeowners + +* Toshi proposed Tet Chiba and Fernando in addition to Toshi (current codeowner). +* Ludovic requested to add Gilles Renoux, Orange. Toshi will ask Administrators to add three. [AI03] + +## Scope Proposal + +* Toshi proposed Scope as [PR #6 Update README.md with modified Scope](https://github.com/camaraproject/KnowYourCustomer/pull/6) +* Toshi showed the PR explaining Scope is part of the first milestone (Milestone 4). There were opinions below: + * Other subprojects’ Scope have just little or very high level. Maybe depends on User Story. (Ludovic) + * It is important to set high level scope considering global market. No need for user consent as high level scope, as Match is sometimes legitimate and country dependent. Email address is one of the important attributes. (Huub) + * Scope should be minimum, and details should be discussed and agree in User Story and attributes discussion. (Efthymios) + * Don’t think ‘limited to 4G and 5G’ is needed. (Javier) +* As conclusion, Toshi to modify the PR #6 with concrete attributes e.g. Mobile phone number removed and consent related text removed. [AI04] + +## User Story – initial proposal + +* Toshi explained User Story is part of the first milestone (MS4), and showed a pptx material briefly explaining use case and flow of KDDI’s KYC-Match and KYC-Fill-in services aiming at it being used for base of User Story work. +* Ludovic suggested to look at the User Story of CarrierBillingCheckOut subproject as it is very good, and then he accepted volunteering work to draft User Story of KnowYourCustomer (KYC-Match and KYC-Fill-in), which was thanked for by Toshi and other members. +* Ludovic told that Gilles, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, would upload a PR for User Story after becoming one of the codeowners. [AI05] + +## AOB + +* Next meeting: November 14th, 0900-1000 CET + + +## Action Items + +* **AI#01.01** Toshi to correct dates of Milestone 4 & 5 in the proposed timeline Excel sheet and distribute to the subproject. + +* **AI#01.02** Toshi to distribute Meeting link for the regular meetings via ML, and also to incorporate the information on the regular meetings into GitHub KnowYourCustomer page. + +* **AI#01.03** Toshi to ask Administrator to add Tet Chiba, Fernando and Gilles Renoux, Orange to KnowYourCustomer codeowners. + +* **AI#01.04** Toshi to modify the PR #6 with concrete attributes e.g. Mobile phone number removed and consent related text removed. + +* **AI#01.05** Gilles Renoux, Orange, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, to upload a PR for User Story draft after becoming one of the codeowners. + +* **AI#01.06** Toshi to share meeting materials shown during the meeting. + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14.md new file mode 100644 index 0000000000000000000000000000000000000000..ec6328ebecb9c1b26d76561e796655afd9a85a12 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-14.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-11-14 + +*Tuesday, November 14th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Scope Discussion +* User Story Discussion +* Next Steps +* AOB + +The Agenda was approved. + +## New Member + +* Daniel Dierich introduced himself, as it was his first time to attend the KnowYourCustomer meeting. + +## Review MoM & Actions + +* MOM 2023-10-31 draft was approved. PR #11 can be merged and closed. +* All the Action Items at the first meeting AI#01.01 ~ 06 were marked 'closed', though some would be confirmed in the later agenda. + + +### Review Issues & PRs + +* [Issue #7 Age Verification API](https://github.com/camaraproject/KnowYourCustomer/issues/7) + * Toshi explained that one of the GSMA’s new API proposals 'Age Verification' will be discussed in the CAMARA TSC on Thursday this week or later and that it will be approved and assigned to KnowYourCustomer subproject, and then asked members' views. + * There were various views. For example, some said that Age Verification should be included in KYC Match API as one of its attributes, and some said that Age Verification should be an independent API from KYC Match because their use cases are different and their regulation on personal information protection tend to be different. + * Members' consensus was that as Age Verification API is useful, we are happy to welcome Age Verification API work, and that it should be a separate API from KYC Match API. +* For other issues/PRs, description in the meeting document were reviewed and approved. + +## Scope Discussion + +* Scope was approved as PR #6. +* Stefano commented that he has commented/ will comment to PR #2 and depending on how his comments would be treated, he might want to modify the current scope text, but that the current scope text is fine with him now. + +## User Story Discussion + +* Gilles drafted User Stories for KYC Match and KYC Fill-in as [PR #13](https://github.com/camaraproject/KnowYourCustomer/pull/13) last week, and Toshi has made comments just before the meeting and Gilles has already reflected the comments to PR #13. However, as members requested for time to review it, the PR was kept open for further discussion. +* All members were requested to review the User Story drafts PR #13 in order to approve the User Story by or at the next meeting. [AI 01] + + +## User Story – initial proposal + +* Toshi explained User Story is part of the first milestone (MS4), and showed a pptx material briefly explaining use case and flow of KDDI’s KYC-Match and KYC-Fill-in services aiming at it being used for base of User Story work. +* Ludovic suggested to look at the User Story of CarrierBillingCheckOut subproject as it is very good, and then he accepted volunteering work to draft User Story of KnowYourCustomer (KYC-Match and KYC-Fill-in), which was thanked for by Toshi and other members. +* Ludovic told that Gilles, a co-worker of Ludovic’s and a KnowYourCustomer maintainer, would upload a PR for User Story after becoming one of the codeowners. [AI05] + +## Next Steps +* Toshi's proposal to start discussion about Flows and Parameters (Milestone 5) on GitHub as well as to start discussion about YAML in parallel, as they are related in general and we need to accelerate our discussion, was accepted. +* Toshi is to create issues for Flow discussion and Parameter discussion. [AI 02] +* Members were informed that there have been three YAMLs uploaded as PRs; [PR #2](https://github.com/camaraproject/KnowYourCustomer/pull/2) Telefonica's KYC Match, [PR #15](https://github.com/camaraproject/KnowYourCustomer/pull/15) KDDI's KYC Match and [PR #16](https://github.com/camaraproject/KnowYourCustomer/pull/16) KDDI's KYC Fill-in. + +## AOB + +* Stefano proposed to add calculating match score feature to KYC Match API, as it is a very useful feature according to Hutchison's experience. +* Javier supported the idea of adding the feature, however, it will make our API work complex, so, it would be better to move the feature to the next version and keep the initial version simple. +* Tet seconded Javier’s comment, adding that KYC Match's first phase should be simple True/False response feature and Stefano's proposal should be tackled in the future versions. +* Members agreed that calculating match score feature would be discussed in the future versions. Toshi would consider how to note it, e.g. creating API's feature roadmap, creating an issue. [AI 03] +* Daniel asked the conclusion about Age Verification API at today's meeting. Toshi explained that it would depend on TSC meeting to be held on this Thursday and that it is likely that the API would come to KnowYourCustomer subproject. +* Huub asked if there was the agreed Attributes list and commented that KYC Attributes are different in each country, adding unique examples in the Netherlands. Toshi replied there is no agreed list yet and it should be discussed in the Parameters discussion. Gilles commented that User Story draft has some example attributes. Fernando commented that we should define compromised common properties. +* Next meeting: November 28th, 0900-1000 CET + +## Action Items + +* **AI#02.01** All members were requested to review the User Story drafts PR #13 in order to approve the User Story by or at the next meeting. + +* **AI#02.02** Toshi is to create issues for Flow discussion and Parameter discussion. + +* **AI#02.03** Toshi would consider how to note "calculating match score feature”, e.g. creating API’s feature roadmap, creating an issue. + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28.md new file mode 100644 index 0000000000000000000000000000000000000000..d991bdab757ba0bd09fe2a98ac88f7e3c231cb44 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-11-28.md @@ -0,0 +1,82 @@ +# CAMARA KnowYourCustomer meeting – MOM-2023-11-28 + +*Tuesday, November 28th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT +* Kazuma Kamiyama, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* User Story Discussion +* Parameters Discussion +* Next Steps including API Documentation +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MoM 2023-11-14 draft was approved. PR #17 can be merged and closed. +* Actions: + * AI #02.01 has been closed. + * AI #02.02 is to be closed today. + * AI #02.03 is kept open. + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show Issues and PRs status, which were noted. + +## User Story Discussion + +* Discussion on User Story PR #13 has been ongoing on GitHub. Discussion point is whether Match Score related phrases are included or not. Toshi proposed not to include them before the meeting to conclude the User Story, based on comments that the User Story should reflect the current scope of the API. +* During the meeting, Stefano commented that it would be better to include potential new functionality like Match Score in the User Story. However, Huub commented that we should be careful to include Match Score, because there are potential issues for Match Score, i.e., for example, there are many ways and solutions for Match Score and also some additional solution like Hashing should be introduced in terms of Privacy protection. +* As conclusion of the discussion, Match Score still needs to be discussed more in the future release, so, it was decided that Match Score related phrases will be incorporated into the User Story when it is discussed. Thus, the latest version of the User Story was agreed, and PR #13 can be merged and closed. + +## Parameters Discussion + +* To conclude our Parameter discussion, Toshi has created the list of our discussion points on the Parameter. +* On Bullet No.1 'How to handle some country/market specific attributes e.g. name reading, user information, idDocument', User information was discussed by using most of the remaining meeting time. +* There were several comments on User information as below (not exhaustive) : + * Same as KDDI, many operators have Subscriber (who has contract with operator) and User (who actually uses the mobile terminal). However, Huub commented that it is not understandable that there are just a few attributes for User, and that there should be the same attributes for User as for Subscriber. He further commented that it may be better to have two different APIs, i.e. one for Subscriber information match and one for User information match. + * Javier commented that customer needs are only for Subscriber information match, or there is no need to differentiate Subscriber and User and it is needed to simply match information like phone number, name, address etc. + * Toshi commented that KDDI is providing KYC-Match API with User information for Name, Name reading and Birthdate as commercial service, and that typically Subscriber is a parent and User is his/her child, and User’s other information is not provided (no customer needs), e.g. User's address is supposed to be the same as Subscriber’s. But there was a comment from Huub that this is not the case and that Even if User is a child of Subscriber, User (the child) may have a different address and other information separate from Subscriber's. +* Regarding Bullet No.1 for User information, KDDI was to consider how it could be handled and get back to the group. [AI #03.01] +* Regarding Bullet No.2, it was agreed to use the camelCase notation for parameter/attribute names, to follow the CAMARA API Design Guidelines . +* Due to time limitation, other discussion points could not be covered, so, Toshi will upload them on GitHub [AI #03.02] and all group members are requested to review and discuss them. [AI #03.03] + +## Next Steps + +* There was Toshi’s proposal to start discussion about API documentation, sharing proposed Skeleton based on QoD v0.8.0’s documentation. +* Toshi will upload it on GitHub as issue/PRs [AI #03.04] and all group members are requested to review and discuss them. [AI #03.05] + +## AOB + +* Next meeting will be December 12th (Tue) 0900-1000 CET. +* As we need more progress, we will have another meeting on December 19th (Tue) potentially. Time to be confirmed checking DeviceLocation regular meeting. + +## Action Items + +* **AI #03.01** Regarding the Parameter discussion, for User information, KDDI is to consider how it is handled and get back to the group. + +* **AI #03.02** Regarding the Parameter discussion, several discussion points could not be covered, so, Toshi will upload them on GitHub for discussion. + +* **AI #03.03** Further to AI #03.02 above, all group members are requested to review and discuss them. + +* **AI #03.04** To start working on API Documentation, Toshi will upload issue/PRs on GitHub related to it for discussion. + +* **AI #03.05** Further to AI #03.04 above, all group members are requested to review and discuss them. + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12.md new file mode 100644 index 0000000000000000000000000000000000000000..6851a7fa3eb2a9a05b783add9d27a899ddfb8a63 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-12.md @@ -0,0 +1,150 @@ +# CAMARA KnowYourCustomer meeting - MOM-2023-12-12 + +* Tuesday, December 12th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Daniel Dierich, DT +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Revised timeline +* KYC Match +* KYC Fill-in +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MoM 2023-11-28 draft was approved. PR #20 can be merged and closed. +* Actions: + * Closed: AI#02.02, AI#03.01, AI#03.02, AI#03.03 + * Kept open: AI#02.03, AI#03.04 + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. + +## Revised Timeline + +* Revised timeline was shared on Page 7 in the agenda slides. The completion date of the initial version had been changed from December 8th to December 22nd. Toshi mentioned that he had spoken to GSMA and that they accepted the change. +* Target dates for some milestones are as below: + * Parameters agreed: ~December 12th (today) + * YAML completed: ~December 19th + * API documentation completed: ~December 19th + * Initial version published: ~December 22nd +* It was agreed that the next subproject meeting would be held on December 19th, 09-10 CET. +* Toshi asked team members whether the meeting time is ok, because the time is the same as Device Location meeting. The team members confirmed the meeting time is OK. Though one of two Telefonica regular members cannot attend, the other will cover. + +## KYC Match +## (1) Parameter discussion: Issue #18 + +* Are all the parameters optional? (DT) ->That is our understanding. (Toshi) +* Too many parameters. Should reduce the number. (TEF) +* It may be too many, but it should be ok as every parameter is optional. (KPN) +* Several parameters included in the list will be used in certain markets only. Naturally the list should include only parameters to be used commonly. (TEF) +* In terms of name, KPN thinks hashed initials are very useful so as to increase matching rate of First name and Family name. According to KPN's experience, that is effective not only for the Netherlands but also other markets. (KPN) +* Currently we are supposed to consider plain text only; not hashing. (TEF) +* To comply with GDPR, operators in the Netherlands always use hash, so parameters to be used for hash mode are required. (KPN) +* In Germany, operators always use hash. (DT) +* Same in UK. Same in Italy. It is better to think in European countries hash is always necessary. (Hutchison) +* Not necessary in Spain. The subproject has agreed that hash will be worked on in the future versions. (TEF) +* Not necessary in France. (Orange) +* There is no problem without hashing in Japan. (KDDI) +* Does anyone know Number Verification API's case, in terms of GDPR? (KDDI) ->Similar discussion is ongoing, I think. (KPN) +* As the team members know, the team members have agreed that additional features such as match scoring and hashing will be discussed in future versions. So **our first version is only for plain text mode. (Toshi) ->Agreed. (All)** +* It is fine, but in the Netherlands, plain text mode will not be used, so, some parameters that KPN has proposed to add for hash mode can be removed from the list for the initial plain text mode version. They are 'givenNameInitial' and 'middleNamesInitials'. (KPN) + + +* Is 'mainPhoneNumber' needed? As the group has agreed that Subscriber/User differentiation concept will be considered in the future versions, the current assumption should be that there is only one phone number. (TEF) +* Because KDDI's current implementation for providing commercial service uses 'mainPhoneNumber', KDDI would like to have it included, but as it seems to be unacceptable by the group, KDDI can compromise and agree to remove it from the list. (KDDI) + + +* There are two items 'cp_id' and 'service_id' included in the list. Don't understand they are needed. (Orange) +* As I have answered on GitHub, KDDI uses these two for 3rd party/API user identity, in addition to that included in the Access Token. They are not pure KYC parameters, but they are used for KDDI's implementation and existing service, so, KDDI would like to have them included in the list, if possible. (KDDI) +* Orange is not comfortable with them, as they are not KYC parameters. (Orange) +* It is true that they are not KYC parameters, but cp_id, which stands for 'content provider id', is used to identify 3rd party/API user, and service_id is used to identify a service brand for the 3rd party/API user's brands. (KDDI) +* If you want to use this kind of information, you can have it in the HTTP header and deal with it by API GW. It should not be in the list. (Hutchison) +* It is understood that opposing opinions against cp_id and service_id seem to be strong among the group members, as they are country/market specific and non-pure-KYC parameters. KDDI can compromise and agree to remove cp_id and service_id from the list. (KDDI) +**->Parameters for KYC Match API was agreed, as Issue #18 comment https://github.com/camaraproject/KnowYourCustomer/issues/18#issuecomment-1853339192.** + +## (2) KYC Match Request/Response parameter/attribute suffix discussion: Issue #22 + +* Final proposal: Request – no suffix, Response – add 'Match' (Orange proposal). +* Don't think it adds value. (TEF) +* OK to add Match to Response. Can differentiate Request and Response. (Hutchison) +* Useful. (KPN) +* As Orange, Hutchison, KPN and KDDI support "Request – no suffix, Response – add Match", I think the group can agree with it. (KDDI) +* Still don't think it adds value. (TEF) +* Better to look at Mobile Connect case. Suffix is not necessary, but adding suffix seems to work for application developers. (KPN) +* If all members other than TEF are happy with it, TEF can stop opposing. (TEF) +* Appreciated. (KDDI) + +**->Suffix to Parameters/attributes for KYC Match API was agreed, as below:** +| **attribute** | **Match Request** | **Match Response** | +| ------- | ----------------- | ------------------ | +|**attribute** | attribute | attributeMatch | +|**e.g. given name** | givenName | givenNameMatch | + +## (3) KYC Match API Error Response Codes discussion: Issue #24 + +* Final proposal is in Issue #24. Basically the response codes included in the TEF's initial YAML and those included in the KDDI's initial YAML are merged. +* Need some time to review the final proposal. (TEF) +* **All members are requested to review the response code final proposal (Issue #24) by COB Friday 15th Dec. [AI#04.01]** + +## (4) KYC Match API YAML definition: PR #27 + +* KDDI has proposed the consolidated YAML definition created as PR #27, which is based on TEF's YAML initial proposal, KDDI's YAML initial proposal and the group's past discussions. But currently no description added. (KDDI) +* **Toshi is to modify the consolidated YAML definition based on today's outcome for KYC Match API. [AI#04.02]** +* **All members are requested to review the consolidated KYC Match API YAML definition proposal (PR #27) by COB Friday 15th Dec. [AI#04.03]** +* Target date for KYC Match API YAML completion: 19th December (Tue) + +## KYC Fill-in + +* Regarding KYC Fill-in API, proposals on Parameters/Attributes, Parameter/Attribute suffix, Error Response Codes etc. have been input by KDDI in Issue #23, and there have been some discussions. (KDDI) +* **All members are requested to review the proposals in Issue #23 by COB Friday 15th Dec. [AI#04.04]** +* **Toshi to modify Parameters/Attributes proposal in Issue #23 based on today's KYC Match discussion outcome. [AI#04.05]** +* Same as KYC Match, KDDI has proposed the consolidated YAML definition created as PR #28, which is based on KDDI's YAML initial proposal and the group's past discussions. But currently no description added. (KDDI) +* **All members are requested to review the consolidated KYC Fill-in API YAML definition proposal (PR #27) by COB Friday 15th Dec. [AI#04.06]** +* Target date for KYC Fill-in API YAML completion: 19th December (Tue) + +## Next Steps + +* Target date for KYC Match and KYC Fill-in API documentation: 19th December (Tue) +* **Toshi to create Issue/PR for this. [remaining AI#03.04]** + +## AOB + +* **Next meeting: 2023/12/19(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #04.01** All - Review KYC Match API Error Response (Issue #24); due COB Friday 15th December + +* **AI #04.02** Toshi - Update KYC Match API Consolidated YAML definition proposal based on the outcome of the Tuesday's meeting + +* **AI #04.03** All - Review KYC Match API Consolidated YAML definition proposal (PR #27); due COB Friday 15th December + +* **AI #04.04** All - Review KYC Fill-in API specifications proposal (e.g. parameters/attributes) (Issue #23); due COB Friday 15th December + +* **AI #04.05** Toshi - Update KYC Fill-in API specifications proposal (e.g. parameters/attributes) based on the outcome of the Tuesday's meeting + +* **AI #04.06** All - Review KYC Fill-in API Consolidated YAML definition proposal (PR #28); due COB Friday 15th December + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19.md new file mode 100644 index 0000000000000000000000000000000000000000..124775ff2b3dca15d6e1453905eeb4611deb8ce8 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2023-12-19.md @@ -0,0 +1,104 @@ +# CAMARA KnowYourCustomer meeting - MOM-2023-12-19 + +* Tuesday, December 19th, 2023 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Timeline +* KYC Match (to complete the initial YAML and the API document) +* KYC Fill-in (to complete the initial YAML and the API document) +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2023-12-12 draft (PR #20) has been approved and merged. +* Actions: + * Closed: AI#02.03, AI#03.04, AI#04.01, AI#04.02, AI#04.03, AI#04.04, AI#04.05, AI#04.06 + * Kept open: None + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. + +## Timeline for the initial version + +* Reviewed the timeline: + * YAML completed: ~December 19th (TODAY) + * API documentation completed: ~December 19th (TODAY) + * Initial version published: ~December 22nd + +## KYC Match + +* Toshi asked members if there are any remaining issues to discuss at the meeting, after mentioning that he understands our discussions on GitHub since our last meeting have cleared all Issues/PRs. +* There was no comment, and it was confirmed that PR #27 (Match YAML) and PR #31 (Match API Document) could be approved and merged. + +## KYC Fill-in + +* There were two remaining issues. +* **Issue #1: in PR #28 (Fill-in YAML), there is a proposal to add “Phone Number” (or MSISDN) to the Fill-in request body.** + * Members understood by GitHub discussions that putting Phone Number into the request body is not necessary, because it can be retrieved from 3-Legged AuthN/AuthZ/ConsentCapturing processes of this API. On GitHub discussions, Orange explained that it is needed for 2-Legged AuthN/Authz. KDDI explained during the meeting that CAMARA/Open Gateway have decided that 3-Legged AuthN/AuthZ processes are required for APIs touch user privacy information including KYC Match/Fill-in APIs. + * If there is no Phone Number in the request body, it will degrade usability of the API. Also, it is better to have Phone Number when it comes to combination with other APIs. It is not understandable why KDDI thinks it is not needed? (DT) + * More than one phone number is used for IoT Devices and Family Member service case, so, it is better to add “Phone Number” to the request body to show which phone number is the target phone number for the KYC Fill-in request, which leads to better usability. (DT) + * The concept of more than one phone number was proposed by KDDI before, and after the group discussion, it was not adopted and left for future enhancement because it will make things complicated. So, if it is related to more than one phone number, it should be discussed in the future release. So, for our initial version, is it ok that Phone Number attribute is not included in the request body? (Toshi) + * Agreed. (DT, Orange, Telefonica) + +* **Issue #2: in PR #32 (Fill-in API Document), there is a question by Orange about KDDI proposed KYC Fill-in API operation/ service sequence; 3rd parties should make contract with MNO (KDDI) for the API use, when 3rd parties shou ld decide which information/ attributes they will receive by an API call, and the 3rd party ID, which a 3rd party is given by MNO when making contract, should only be included in the Fill-in API request body.** + * As 3rd party Id can be retrieved by AuthN/AuthZ/Consent Capturing processes (Client ID), there is no need to include 3rd party Id in the request body. (Orange) + * If the 3rd Party Id is not included in the request body, there would be no attribute parameter in the Fill-in API request body. Is it no problem? (Toshi) + * No problem. (Orange) + * KDDI’s Fill-in API operation/ service sequence forces 3rd parties to decide which information/ attributes they can receive by an API call. This is for better security / privacy protection. MNO can control which information/ attributes a 3rd party will receive, considering its scale, business areas, credit quality and so on. (KDDI) + * Because there is no information sent from a 3rd party to MNO in the request body, it is up to the MNO to decide which information/attributes the 3rd party will receive. Is this OK? Also, in terms of security and privacy protection, the MNO should be responsible for that. Is this OK, as well? (Toshi) + * OK. (Orange) + * I will write down these somewhere in the API document and/or the YAML description. (Toshi) + * As the 3rd party id can be retrieved by AuthN/AuthZ/Consent Capturing processes, it seems it is the same situation as the Phone Number. So, it should be discussed in the future releases. (DT) + * OK. (KDDI) + +## Next Steps + +* **KYC Match API:** as the YAML (PR #27) and the API Document (PR #31) are fixed, these two PRs are to be merged within today as it is. + * **Codeowners (Fernando, Gilles) to approve the PRs. [AI#05.01]** + * **Then Toshi to merge the PRs. [AI#05.02]** + +* **KYC Fill-in API:** the YAML (PR #28) and the API Document (PR #32) will be modified according to today’s outcome. Then the modified PRs will be merged within today. + * **Toshi to modify the YAML and the API document according to today’s outcome [AI#05.03]** + * **Then Codeowners (Fernando, Gilles) to approve the PRs. [AI#05.04]** + * **Then Toshi to merge the PRs. [AI#05.05]** + +* **Next steps after the Christmas Break:** + * Initial version agreed today (v0.1.0): Error correction, missing information, improvement of API description + * Next version (v0.2.0): leftover issues, new features, functional enhancement + * Age verification API to start + +## AOB + +* **Next meeting: 2024/1/9(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #05.01** For KYC Match API, Codeowners (Fernando, Gilles) to approve PR #27 and PR #31 +* **AI #05.02** Then Toshi to merge the PRs +* **AI #05.03** For KYC Fill-in API, Toshi to modify the YAML and the API document according to today’s outcome +* **AI #05.04** Then Codeowners (Fernando, Gilles) to approve the modified PRs. +* **AI #05.05** Then Toshi to merge the approved PRs. + + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09.md new file mode 100644 index 0000000000000000000000000000000000000000..b5e8c6d537807638b1f042c79ed6f1f97910eee7 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-09.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-01-09 + +* Tuesday, January 9th, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* Next Steps +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2023-12-19 draft (PR #33) has been approved and merged. +* Actions: + * Closed: none + * Kept open: none + +### Review Issues & PRs + +* Page 5 (Issues) and Page 6 (PRs) in the agenda slides show current Issues and PRs, which were noted. It was agreed that all the current issues and PRs were for v0.1.0 and could be closed. **->To close all the issues and PRs. (Toshi) [AI#06.01]** + +## Next Steps + +**(1) v0.1.0** +* Making the -rc version and the release version as well as making the release branch & Changelog.md is just a common process. Don’t think there is any error correction needed and any missing information. Concern is that parameter/attribute descriptions are enough or not. (Telefonica) + +* Agree. We may need to add parameter/attribute descriptions. Will create an issue/PR for this. (Toshi) **->To create an issue/PR for adding parameter/attribute descriptions (Toshi) [AI#06.02]** + +* Regarding "application/json;charset=utf-8 or application/json" and "#/components/headers/x-correlator", **Toshi will check Commonalities discussion in order to decide if there is anything to do for v0.1.0. (Toshi) [AI#06.03]** + +**(2) v0.2.0** + +* Toshi listed up leftover issues, new features, functional enhancement etc. which were identified during the v0.1.0 discussions. There was no comment to delete any items from the list, so, all items were regarded as v0.2.0 candidate items. **->Toshi to create issues for each item. (Toshi) [AI#06.04]** + +* Regarding the item (7), Mobile Connect-like Match response (Y, N-NA, N-AV, N-AD), **DT will discuss it internally with their experts about Error Reponses etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (DT) [AI#06.05]** + +* Regarding the item (9), Gender attribute, **Telefonica will discuss it internally with their experts about Privacy etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (Telefonica) [AI#06.06]** + +* Regarding the item (11), **Toshi will arrange for OIDF to make a presentation about their eKYC-IDA activity during the next KnowYourCustomer SP meeting (or a later meeting). (Toshi) [AI#06.07]** + +* Regarding the item (11), having been asked, DT replied that Dawid Wrobleswski takes part in the Identity and Consent Management WG, and that DT takes part in OIDF but it is not clear that DT is engaged actively in eKYC-IDA. (DT) + +**(3) Age Verification API** + +* Orange wants to start Age Verification discussion, but Gilles is not the person responsible for the topic. Toshi has asked GSMA to identify the responsible person and is waiting for their reply. + +## AOB + +* **Next meeting: 2024/1/23(Tue) 0900-1000 CET.** Hopefully OIDF’s eKYC-IDA presentation will be included. + +* DT asked to add 'Efthymis Isaakidis, DT' as attendee to MoM-20231212 and MoM-20231219. (DT) **->Toshi to create PRs. (Toshi) [AI#06.08]** + +## Action Items + +* **AI #06.01** It was agreed that all the current issues and PRs were for v0.1.0 and could be closed. ->To close all the issues and PRs. (Toshi) + +* **AI #06.02** For v0.1.0, to create an issue/PR for adding parameter/attribute descriptions (Toshi) + +* **AI #06.03** Regarding “application/json;charset=utf-8 or application/json” and “#/components/headers/x-correlator”, Toshi will check Commonalities discussion in order to decide if there is anything to do for v0.1.0. (Toshi) + +* **AI #06.04** For all the listed up items, Toshi to create issues for each item as v0.2.0 candidate items. (Toshi) + +* **AI #06.05** Regarding the item (7), Mobile Connect-like Match response (Y, N-NA, N-AV, N-AD), DT will discuss it internally with their experts about Error Reponses etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (DT) + +* **AI #06.06** Regarding the item (9), Gender attribute, Telefonica will discuss it internally with their experts about Privacy etc. and will give the subproject their feedback if this item needs to be discussed for v0.2.0 or not. (Telefonica) + +* **AI #06.07** Regarding the item (11), Toshi will arrange for OIDF to make a presentation about their eKYC-IDA activity during the next KnowYourCustomer SP meeting (or a later meeting). (Toshi) + +* **AI #06.08** Toshi to create PRs for adding ‘Efthymis Isaakidis, DT’ as attendee to MoM-20231212 and MoM-20231219. (Toshi) diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23.md new file mode 100644 index 0000000000000000000000000000000000000000..7b66794904a83e9b5c0f1998703da80cd60c0cc6 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-01-23.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-01-23 + +* Tuesday, January 23rd, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + +## Review MoM & Actions + +* MOM 2024-01-09 draft (PR #41) had been approved by the codewoners, however, an error in writing was found in Action Items. It was corrected a few hours before the meeting and the codeowners were requested to approve it again. + +* Actions: + * Closed: AI #06.08 + * Kept open: AI #06.01, #06.02, #06.03, #06.04, #06.05, #06.06, #06.07 + +### Review Issues & PRs + +* [Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18) KYC Match - Compare specifications + * (for v0.1.0) Javier TEF and Huub KPN commented in Github. Once AI#06.02 has covered these comments, this issue will be closed. + +* [Issue #37](https://github.com/camaraproject/KnowYourCustomer/issues/37) Include API description in yaml + * (for v0.1.0) Ongoing. PR #44 and PR #45 have been created by Toshi KDDI. Once these two PRs have been merged, this Issue can be closed. + +* [Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38) Proposition of design evolution + * Ongoing discussion. + +* [Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39) Polymorphism and discriminator for specific requirement + * Ongoing discussion. PR #43 has also been created by Gilles Orange, but it is not-to-be-merged. Aim is to identify Market/Country specific attributes in yaml, by using Polymorphism and discriminator. Device Location uses similar methods. (Orange) + * This way may make the API more complicated. There may be other ways than something in yaml, e.g. routing solutions with aggregators. (HUT) + * How aggregators know the market/country could be an issue. (TEF) + * As the discussion was very good but it was difficult to catch the details, Toshi KDDI requested Stefano HUT to make comments in the GitHub. + +* [Issue #40](https://github.com/camaraproject/KnowYourCustomer/issues/40) CHANGELOG.MD + * (for v0.1.0) Ongoing. CHANGELOG.MD is needed for v0.1.0 release. To be reviewed and corresponding PR to be created. + +* [PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43) Match API Design evolution proposal + * PR related to issue #39. Ongoing. Please discuss in Issue #39. + +* [PR #44](https://github.com/camaraproject/KnowYourCustomer/pull/44) Update kyc-match.yaml to include API description in yaml + * (for v0.1.0) Related to issue #37. Quick merge is expected, as it is just to make API description kyc-match.md included in the yaml, but SP members are requested to review. [AI#07.01] + +* [PR #45](https://github.com/camaraproject/KnowYourCustomer/pull/45) Update kyc-fill-in.yaml to include API description in yaml + * (for v0.1.0) Related to issue #37. Quick merge is expected, as it is just to make API description kyc-fill-in.md included in the yaml, but SP members are requested to review. [AI#07.02] + +## AOB + +* Efthymis DT raised an issue as a v0.2.0 topic. + * In terms of connection with Channel Partner, customer information protection could be an issue. In principle, user's authorization mechanism exists, but malicious application developers or those who access illegally might cause leak of customer information. Data minimization should be considered, and it is necessary to introduce some mechanism, with which only limited information can be accessed by application developers or aggregators, based on their use cases shared with operators when onboarding. This is both for KYC Match and KYC Fill-in APIs. (DT Efthymis) + * One solution would be to decide which personal information a channel partner can be access between a channel partner and an operator. Another solution would be hashing to avoid transmitting KYC information as plain text. (HUT Stefano) + * Regarding hashing, DT's implementation uses hashing for part of Match and Fill-in as the necessary feature. (DT Efthymis) + * Toshi asked Efthymis to create an issue for a new discussion topic, and Efthymis agreed to do it. [AI#07.03] + * Toshi explained that KDDI's Fill-in service has a process that when a third party makes contract with KDDI for the Fill-in service, both decide what information the third party can get by calling Fill-in API. A third party puts its 3rd party ID in the Fill-in API request body, and on receiving the 3rd party ID, KDDI provides limited information based on the contract. This measure was proposed for Fill-in v0.1.0, but it was not accepted by the group. (KDDI Toshi) ->It could become a solution. (DT Efthymis) + * Another potential solution is to use "scope" to limit information that the Channel Partner can handle. (DT Efthymis) + * Using "scope" has been discussed in CAMARA Identity and Consent Management WG (ICM). It relates to CIBA Flow and Operate API for onboarding. But the ICM documentation is still in progress. It is recommended for KYC APIs to introduce the mechanism for privacy protection once the ICM documentation has been matured enough. (DT Rafal) + +* **Next meeting: 2024/2/6(Tue) 0900-1000 CET.** OIDF's eKYC-IDA presentation is planned. + +## Action Items + +* **AI #07.01** SP members are requested to review PR #44. (All SP members) + +* **AI #07.02** SP members are requested to review PR #45. (All SP members) + +* **AI #07.03** DT Efthymis is to create a Privacy Protection related issue for a new discussion topic. (DT Efthymis) + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06.md new file mode 100644 index 0000000000000000000000000000000000000000..0492a110f758f306c3b9d1f0414e44b87ba8d5ee --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-06.md @@ -0,0 +1,87 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-02-06 + +* Tuesday, February 6th, 2024 + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica +* (Guest) Mark Haine, OIDF +* (Guest) Kosuke Koiwai, OIDF/KDDI + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + +## Agenda + +* Review MoM & Actions +* Guest presentation – OIDF eKYC-IDA +* Review Issues & PRs +* AOB + +The Agenda was approved. + +Javier Carro Telefonica commented that Telefonica would like to resolve open issues for v0.1.0 quickly and release v0.1.0 soon, due to requirement from their product team and business team. + +->Toshi agreed with early release of v0.1.0, and proposed to discuss it after OIDF presentation. + +## Guest presentation – OIDF eKYC-IDA + +* Mark Haine, OIDF eKYC-IDA WG chair, introduced their activity using his presentation materials. (The presentation materials have been shared with the subproject members after the meeting, by email circulation and by uploading to the repo.) +* It was mentioned that three products exist in UK and Germany etc. How is Consent Management dealt with? (Telefonica) +* ->In Germany, Yes.com provides Identity Assurance information to a large number of banks. Consent confirmation attribute is used in OIDC process. (Mark) +* How about others? (Toshi) +* ->Another case is Government Citizen identity system. OIDC plus sharing consent confirmation results. (Mark) +* ->Another case is ConnectID in Australia. Like Yes.com, it provides Identity Assurance information to banks. (Mark) +* ->Conformance tests were completed in these cases. (Mark) +* If CAMARA KYC-Match and KYC-Fill-in APIs adopt OIDC eKYC-IDA, what benefit it would receive? (Toshi) +* ->If the APIs are used for many use cases, interconnectivity will be improved, in terms of data structure. When new objects to share with application developers appear, it is easier to utilize Meta data etc. It would be possible to change range of data to share with each application developer, so it will lead to data minimization. (Mark) +* If there is a specific use case with CAMARA/Open Gateway, Mark can create and share example response messages. (Mark) +* Toshi asked Mark to continue information sharing and discussion, and Mark kindly agreed. +* Toshi will an Issue to discussion collaboration with OIDF eKYC-IDA. [AI#08.01] + +## Review MoM & Actions + +* MOM 2024-01-23 draft (PR #48) and Uploading the meeting material (PR #49) are approved and to be merged. + +* Actions: + * Closed: AI #06.01, #06.02, #06.07, #07.01, #07.02, #07.03 + * Kept open: AI #06.03, #06.04, #06.06 + +## Review Issues & PRs + +* Issue #18 KYC Match - Compare specifications (Issue #18) + * (for v0.1.0) To be closed soon, as discussion on description of parameters is closing. + +* Issue #37 Include API description in yaml (Issue #37) + * (for v0.1.0) To be closed, as PR #44 and PR #45 are to be merged. + * Apart from this Issue and related PRs, the remaining issue is the description of parameters, related to Issue #37. Toshi will create corresponding PRs, but as description of parameters in the current YAMLs are not needed to be modified much according to his reading, Toshi thinks the PRs could be simple and approved soon. + * Telefonica requested to complete the remaining issues and release v0.1.0 by end of this week. + * Toshi agreed and told he would create PRs today or tomorrow, and asked all to review the PRs so that they could be approved within this week. + +* Issue #46 and PR # 50 + * (for Age Verification) Gilles Orange pointed out that there has been no comments for Age Verification Issue/PR, and shared his concern that it may not be completed by end of March, which had been requested by GSMA. + * Call for action: all to review the Issue and PR for Age Verification and to be encouraged to discuss actively on GitHub. [AI#08.02] + +## AOB + +* **Next meeting: 2024/2/20(Tue) 0900-1000 CET.** + +## Action Items + +* **AI #08.01** Toshi will an Issue to discussion collaboration with OIDF eKYC-IDA. (KDDI Toshi) + +* **AI #08.02** All to review the Issue and PR for Age Verification and to be encouraged to discuss actively on GitHub. (All) + + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20.md new file mode 100644 index 0000000000000000000000000000000000000000..ca9cb2239835069b4ca68ac7a58e1c3afb01ed3f --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-02-20.md @@ -0,0 +1,100 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-02-20 + +* Tuesday, February 20th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-02-06 draft ([PR #56](https://github.com/camaraproject/KnowYourCustomer/pull/56)) is ready to merge. + +* Uploading the meeting material ([PR #54](https://github.com/camaraproject/KnowYourCustomer/pull/54)) has been merged and it has been uploaded. +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.04, #06.06, #08.01, #08.02 + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – working on error correction and other refinement to create a release version + +* Issue #37 Include API description in yaml ([Issue #37](https://github.com/camaraproject/KnowYourCustomer/issues/37)) +* PR #44 Update kyc-match.yaml to include API description in yaml ([PR #44](https://github.com/camaraproject/KnowYourCustomer/pull/44)) +* PR #45 Update kyc-Fill-in.yaml to include API description in yaml ([PR #45](https://github.com/camaraproject/KnowYourCustomer/pull/45)) + * PR #44 and PR #45 have been approved and merged. + * Thus, including API description into yaml files has been completed, and Issue #37 can be closed. + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) +* PR #51 KYC-Match-Parameter Description Refine ([PR #51](https://github.com/camaraproject/KnowYourCustomer/pull/51)) +* PR #52 KYC-Fill-in-Parameter Description Refine ([PR #52](https://github.com/camaraproject/KnowYourCustomer/pull/52)) + * PR #51 and PR #52 have been approved and merged. + * Thus, refining parameter description in KYC Match and KYC Fill-in yamls has been completed, and Issue #18 can be closed. + +* Toshi KDDI told that he had some difficulty in creating a PR for uploading CHANGELOG.md, but Rafal DT replied that there is not anything different from other file uploading PRs. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing + * Gills Orange has responded to Toshi KDDI's comment. KDDI is to send reply comments. + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. PR #43 has been created by Gilles Orange for Issue #39, but it is not-to-be-merged. + * Gills Orange has responded to Toshi KDDI's comment. KDDI is to send reply comments. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. + * Gills Orange has commented for this issue. KDDI is to discuss internally and comment. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * OIDF Age Verification presentation to be arranged at the next meeting (Marth 5th) + * Gilles Orange has proposed the user story of Age Verification. KDDI and all KYC-SP members are expected to review the proposal. **AI #09.01** + * Huub KPN asked where Age Verification is discussed. ->Toshi replied that it is we KYC-SP that is discussing Age Verification and that Issue #46 is the issue to be looked at. + * Toshi suggested that Liberty Global might have interest in Age Verification, because they nominated Age Verification API for GSMA Open Gateway Product Workstream Drop #3 candidates. + + +## AOB + +* **Next meeting: 2024/3/5(Tue) 0900-1000 CET.** + +* There will be two CAMARA in-person events to held with MWC Barcelona, i.e. CAMARA meet and greet on Day1 at the MWC venue and CAMARA Evening Gathering on Day2 at a nearby hotel. Toshi encouraged all to attend and see each other in Barcelona. + + +## Action Items + +* **AI #09.01** Gilles Orange has proposed the user story of Age Verification. KDDI and all KYC-SP members are expected to review the proposal. (all) + +* **All other remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05.md new file mode 100644 index 0000000000000000000000000000000000000000..6d97c3a38c9be299d0496b42c12abefcc2199680 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-05.md @@ -0,0 +1,106 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-03-05 + +* Tuesday, March 05th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Huub Appelboom, KPN +* Jorge Garcia Hospital, Telefonica +* Kiyoto Shinomura, KDDI +* Kosuke Koiwai, KDDI/OIDF +* Aziz Abouchi, SFR + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda + +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +Note: Presentation on Age Verification by OIDF has been postponed to our next meeting (19th March) or before, due to their unreadiness. + +Note: CAMARA had two events successfully during MWC24. 'Meet and greet' on Monday 26th at a meeting room in Fira Gran Via where MWC24 was held, and 'evening gathering' on Tuesday 27th at a hotel nearby. Hope to meet KYC SP members on another occasion. + + +## Review MoM & Actions + +* MOM 2024-02-20 draft as well as a corresponding PR was not yet created. (Toshi was sorry for that.) + +* Uploading the meeting material ([PR #58](https://github.com/camaraproject/KnowYourCustomer/pull/58)) was created a couple of hours before the meeting, so, review by SP members and approval by the code owners were expected. + +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.04, #06.06, #08.01, #08.02, #09.01(this was added after the Marth 05th meeting) + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – working on error correction and other refinement to create a release version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * It was supposed to be closed together with PR #51 and PR #52, but some discussions were ongoing. ->Need to check if the discussions can be moved to a new issue for v0.2.0. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It was supposed to be closed, but Stefano Hutchison has commented pointing out a new point. ->Need to check if the discussions can be moved to a new issue for v0.2.0., with Stefano who was absent from the meeting. + +* Issue #40 CHANGELOG.MD ([Issue #40](https://github.com/camaraproject/KnowYourCustomer/issues/40)) +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * After Rafal DT's comment at the last meeting on Feb 20th, Toshi successfully created a PR to upload CHANGELOG.MD as a new file, based on the Gilles' draft and modified for inclusion of API description into the yaml. Ready to be approved. + +* A new issue: Country/countryCode/countryName attribute and for countryCode alpha-2 or alpha-3 + * Issue to be created. **AI #10.01 (Toshi)** + +* Telefonica Javier Carro and Fernando proposed to remove 'phoneNumberMatch' attribute from KYC Match yaml, because, if the phoneNumber sent in the Match request is wrong, the process should be terminated by responding Error 403, so phoneNumberMatch becomes always 'true', so there is no need of it. + * Toshi asked Javier Carro and Fernando to create an Issue for that, so that it can be discussed by the SP. Specifically, Toshi told that KDDI needed to discuss internally and would send feedback to the issue. + * ->Telefonica also proposed to resolve this issue quickly by end of the week, so that KYC SP could publish the release version of Match/Fill-in v0.1.0, and then Fernando created the Issue #59 straightaway, and so, all members were requested to review the Issue as quickly as possible. **AI #10.02 (All)** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. PR #43 has been created by Gilles Orange for Issue #39, but it is not-to-be-merged. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * OIDF Age Verification presentation to be arranged at the next meeting (Marth 19th) or before. + + +## AOB + +* **Next meeting: 2024/3/19(Tue) 0900-1000 CET.** + + +## Action Items + +* **AI#10.01**: A new issue to be discussed - Country/countryCode/countryName attribute and for countryCode alpha-2 or alpha-3; Issue to be created. (Toshi) + +* **AI#10.02**: Issue #59 for Telefonica's proposal to remove 'phoneNumberMatch' attribute from KYC Match yaml; KDDI and all KYC-SP members are asked to review the proposal and send feedback as soon as possible; by Friday 8th at the latest. (all) +* **All other remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19.md new file mode 100644 index 0000000000000000000000000000000000000000..98e374369eb2610cd6a367235e1935b089349ad4 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-03-19.md @@ -0,0 +1,130 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-03-19 + +* Tuesday, March 19th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Javier Carro Calabor, Telefonica +* Kazuma Kameyama, KDDI +* Kosuke Koiwai, KDDI/OIDF +* Aziz Abouchi, SFR +* (guest) Mark Haine, OIDF +* (guest) Dima Postnikov, OIDF + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* OIDF presentation re: Age Verification +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## OIDF presentation re: Age Verification + +* Presenters: + * Mark Haine, OIDF + * Dima Postnikov, OIDF +* Mark presented OIDC Advanced Syntax for Claims (ASC) including its concepts and its specification aspects. + * Outline of his presentation is captured at the bottom of this MoM. + * His slide deck has been shared by KYC-SP ML and uploaded to KYC-SP Repo. + * URL link to the current Advanced Syntax for Claims Work Group Draft: https://openid.bitbucket.io/ekyc/openid-connect-advanced-syntax-for-claims.html +* Dima shared how ConnectID AU introduced OIDC+IDA + ASC as a usecase in Australia. + * Outline of his presentation is captured at the bottom of this MoM. + * URL link to ConnectID AU spec: https://cdn.connectid.com.au/specifications/digitalid-identity-assurance-profile-05.html +* All thanked Mark and Dima for their presentation. +* All were requested to provide any feedback on the presentation. **AI #11.01** + + +## Review MoM & Actions + +* Due to lack of time, it was requested to review the related PRs and the actions list. +* MOM 2024-03-05 draft -> [PR #64](https://github.com/camaraproject/KnowYourCustomer/pull/64) +* Uploading the meeting 2024-03-05 material -> [PR #62](https://github.com/camaraproject/KnowYourCustomer/pull/62) +* Actions: + * Closed: AI #06.04, #10.01, #10.02 + * Kept open: AI #06.03, #06.06, #08.01, #08.02, #09.01 + + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Due to lack of time, it was requested to review the related PRs and the actions list. + +### Match/Fill-in v0.2.0 – wip + +* Due to lack of time, it was requested to review the related PRs and the actions list. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing + * Toshi KDDI - As Age Verification API is a GSMA Open Gateway Drop #4 API, we should complete Age Verification v0.1.0 quickly. As Gilles has already created a proposal of the user story on GitHub, it is better for us to agree on the user story first. + * Toshi KDDI - In the Issue #46 discussion on GitHub, I found a problem was shared which I would agree with. The problem is that we verify the age against the contractor / subscriber data, not against the user who is currently using the handset. + * Gilles Orange - The proposal was that, for the initial version, the condition should be the owner of the contract is the user. If not, we cannot verify the age. (Gilles Orange) + * Toshi KDDI - replied that it made sense, adding a note that, during GSMA product portfolio work stream meeting on the day before, someone from Vodafone showed their interest in Age Verification API and asked GSMA for of Orange’s Age Verification API contact. + * Gilles Orange – His colleague may be contacted as they do not know the latest status. They thought we did not make any progress as they did not see anything in the main branch. + * Toshi KDDI – Vodafone also mentioned that they are interested in KYC Match API and together with Hatchison, they are going to do some input of some logic. Stefano may be aware of it. In the GSMA meeting, Toshi replied that any input would be welcome. + +## AOB +* From next meeting, Europe will be in summer time, but some countries including Japan do not have summer time, so we need to agree on our meeting time. As KDDI does not have problem with keeping the same meeting time for Europe and other countries having summer time, it was agreed that our meetings will be held for 0900-1000 CEST. +* **Next meeting: 2024/4/2(Tue) 0900-1000 CEST.** + + +## Action Items +* **AI#11.01**: All were requested to provide any feedback on the OIDF Age Verification presentation. (All) +* **All other remaining AIs** + + +## Appendix + +### Outline of Mark Haine’s presentation on OIDC Advanced Syntax Claims (ASC) +* (Page 1) This presentation was what Daniel Fett presented at OSW last year and adjusted. (OSW: OAuth Security Workshop) +* (Page 2) OIDC advanced syntax for claims was inspired by age verification use case so why he wanted to share this. +* But more than that, extend the use case, much more about requesting and receiving claims. Fine grained control over date delivery. RPs more control over what they get, a number of business reasons. +* Complex data structures, especially from IDA. Need better control of Json hierky claims., OIDC Core 2 levels vs IDA 5+ revels, difficult to control with OIDC mechanism. +* (Page 3) So ASC is no requirement for IDA, on top of any OIDC implementation. +Couple of special allowances for better use of. +* 2 important components, Transformed claims, age verification and others. Selective Abort/Omit. +* (page 4) Transformed Claims. +* (page 5) Usecase identified for Age Verification. Any convention, any version of age verification, over 16 or 18 or 21, varies in some countries. Retirement ages complex. +* Also ended up with transformed claims based on suffix on email, zip code, nationality (if contain multiple nationalities) etc. Allows us to return things derived from the base claims. +* (page 6) Idea: Claims values can be transformed using a small set of functions before any further evaluation is performed. +* (page 7) Example: Age Verification. Definition is above_18, then use – prefix ':' +* (page 8) In the draft spec, there are set of functions can be used, we think this is a decent set. Years_ago is application specific, but other than that is generalized. +* (page 10) We have spent a bit of time for simplification of implementation, IDP can add metadata to say only a subset is supported. Only allowing useful for age verification use case, also allow provide predefined transformed claims. Predefined claims to get above_18, simpler to execute for both parties. +* Also allow OPs to only support PTC. +* (page 11) Another example with PTC, Double colon indicates PTC, we do not need to define what above_18 means in the claims parameter +* (page 12) Another things discussed was UX consideration, show something meaningful to users to get consent is difficult. Worst case scenario say birth date (base claim) is provided. +* (page 14~17) Second feature, slightly more experimental slides. OIDC code feature essential:true, not widely implemented or understood. SAO, enable further data minimization. Allow for elements of the response to be conditionally left out. +We had a bit of troubles, Takahiko Kawasaki discovered a race condition, not deterministic. +* (page 18) What we came up is more flexible way of expressing the SAO feature without the race condition, Use JSON schema based definition +* (page 19) Example, for a verified_claims/claims, if it matches birthdate = 1900-01-01, omit all verified_claims/claims +* Effectively allows us condition, if a particular post code condition, if a post code is not London, omit address, or additional action, abort. Age verification. TSC, over the age of 13, abort the request if the user is under the age of 13. Minimum age of social media. We don’t want to ask users age, but don’t want to receive anything if the use is below 13. +* Come up with more general use such as post code, address, or with IDA, we only want to rely on verified identity if passport has been used or IAL2 and passport. Highly flexible, write conditions. +* Keep complexity under control, discuss taking it quite. Bit further, but decided not to go that far. Looked at some conditional languages, complexity and additional risks, large set of use cases, this set of feature will enable. We decided to not go too far to be a programming language. Relatively simple compared to other ways. +* More feedback will be valuable, trying to move to 1st ID. + +### Outline of Dima Postnikov’s presentation on ConnectID AU +* In AU, building national id infrastructure, ID scheme based on OIDC + IDA to start with, other methods Verifiable presentation. +* Advanced claims specs. In ConnecID Au, we use multiple specs. Not just OIDC+IDA, we ended up mixing multiple. +* Standard OIDC claims, verified_claims, +* Standard - typical name, phone, address etc., Advanced claims, 2 reasons, in future want to provide a lot of metadata. Additional metadata, how was the data verified, how long ago by whom, some non standard claims that OIDC not provide. Clear language over16,18,21,25,65, 18 is mainly used 95%, and bank account details. Lottery payout or insurance claims, telecom mobile number ownership. In future ASC, we will give me everything or nothing. RP don’t want to pay data unless full set. +* In AU, user OIDC + IDA, in future ASC. + +[END] + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02.md new file mode 100644 index 0000000000000000000000000000000000000000..290f2f893dea108f1380262334ae634c35ef80ca --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-02.md @@ -0,0 +1,102 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-04-02 + +* Tuesday, April 2nd, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Efthymis Isaakidis, DT +* Stefano Falsetto, Hutchison +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Axel Nennker, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-03-19 draft -> [PR #68](https://github.com/camaraproject/KnowYourCustomer/pull/68), created on March 29th and asked to be reviewed ->No comments and approved +* Uploading the meeting 2024-03-19 material -> [PR #67](https://github.com/camaraproject/KnowYourCustomer/pull/67), has been approved and merged. +* Actions: + * Closed: None + * Kept open: AI #06.03, #06.06, #08.01, #08.02, #09.01, #11.01 + * AI #08.02 and AI #09.01 are kept open, as both are for asking Team members to review Age Verification Issues and PRs. + * AI #11.01 is kept open, waiting for Team members’ feedback for OIDF Age Verification presentation. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. ->Need to check. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
                                                PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * We are continuing the exchange of opinions on Assurance levels and related matters on GitHub. (Orange Gilles) + * We should check the global situation. In Europe (eIDAS), three levels are defined. (KPN Huub) + * Also, the logic of the matching process needs further in-depth consideration and discussion. (KPN Huub) + * Next week, we will share relevant information. Depending on the subject, there are cases where plain text or hashes are used. (Hutchison Stefano) + * I am participating in a fuzzy logic conference/meeting. (Hutchison Stefano) + * The fuzzy logic discussion pertains to Age Verification as well as KYC Match. (Hutchison Stefano) + * Useful discussion. Please add the comments you made, to Issue #46. (Toshi KDDI) + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. Can user Story be approved? + * How the discussion on Issue #46 is going may require modifications of the draft User Story? (Toshi KDDI) ->Yes, likely. (Orange Gilles) ->So, the draft User Story cannot be approved now. Comments on typos have been input, anyway. (Toshi KDDI) + +* README.md should have Age Verification + * The top page of KYC-SP's GitHub Repo should have Age Verification-related text as part of Scope. (Toshi KDDI) -> Toshi is to draft text. **AI #12.01 (Toshi)** + + +## AOB +* **Next meeting: 2024/4/16(Tue) 0900-1000 CEST.** +* Linux Foundation requested all Camara API subprojects and Working Groups to move their regular calls to Zoom platform. KYC-SP meetings will move to Zoom platform once we are ready for that. + + +## Action Items +* **AI#12.01**: The top page of KYC-SP's GitHub Repo should have Age Verification-related text as part of Scope. Toshi is to draft text. [Toshi] +* **All other remaining AIs** + +[END] + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16.md new file mode 100644 index 0000000000000000000000000000000000000000..8bf4b491f2cd6544f1213da0b94cac585b1913b2 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-04-16.md @@ -0,0 +1,118 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-04-16 + +* Tuesday, April 16th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Surajj Jaggernath, Vodacom +* Rafal Artych, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-04-02 draft -> [PR #72](https://github.com/camaraproject/KnowYourCustomer/pull/72), created on April 12th. ->No comments and approved. +* Uploading the meeting 2024-03-19 material -> [PR #73](https://github.com/camaraproject/KnowYourCustomer/pull/73), has been approved and merged. +* Actions: + * Closed: AI #06.03 + * Kept open: AI #06.06, #08.01, #08.02, #09.01, #11.01, #12.01 + * AI #06.03 was closed, as per Telefonica Fernando's comment that Commonalities WG has concluded on "application/json;charset=utf-8 or application/json" and "#/components/headers/x-correlator" so AI #06.03 can be closed. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. Toshi is to take care of it. **AI #13.01 (Toshi)** + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0? ->This issue is to be closed after being moved to a new issue. Toshi is to take care of it. **AI #13.02 (Toshi)** + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. ->Need to check after the meeting. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
                                                PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->Continue discussion on GitHub + * Huub KPN commented that the Issue includes many items in the list, and that it is better to split the items into each Issue, so that we can decide each item to be discussed, to be closed, or to be delayed. -> Toshi is to create Issues for each item. **AI #13.03 (Toshi)** + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * A new issue for Correction. + * I would change streetNumber to houseNumber. This is not an issue in the Netherlands, but in some countries, e.g. US, they have 1st East St., 2nd East St. 3rd East St. etc., Street Name has numbering, and it may confuse the streetNumber attribute. Proposal is to have streetName, houseNumber, houseNumberExtension.) (Huub KPN) + * In Spain, in residential areas, streetName and streetNumber may be enough, but in the city, streetName and streetNumber can identify the building, where many houses with each houseNumber exist, so streetNumber and houseNumber is different. (Fernando TEF) + * In that case, houseNumberExtension can be used to differentiate in the Netherlands. (Huub KPN) + * In US, streetName has numbering, so, streetNumber attributes may confuse people thinking it is street numbering or houseNumber, they say. (Huub KPN) + * In Spain, streetName is unique, and numbering is not used. (Fernando TEF) + * In France, same. (Gilles Orange) + * If we change streetNumber to houseNumber to solve US’s problem, it may cause other problem with other countries having different systems. (Fernando TEF) + * How about other standardization like Mobile Connect? (Huub KPN) + * Will check TM Forum. (Gilles Orange) + * Will check OIDF. (Toshi KDDI) + * Let’s compare other standardization cases and continue discussion on GitHub. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * It seems to converge into Jaro Winkler as the preferred method for doing fuzzy name logic. That is one conclusion that we can have already. (Huub KPN) + * Yes. (Gilles Orange) + * KDDI is still discussing this internally, and especially is concerned that fuzzy name logic is not needed for Japanese language. (Toshi KDDI) + * It is understood that Japan does not need fuzzy name logic and would use exact match. It can use 100% always for Jaro Winkler. But, in EU market, fuzzy name logic is required. (Huub KPN) + * Understood. From KDDI point of view, it would be better to make fuzzy name logic an optional feature and make Age Verification API workable without it. (Toshi KDDI) + * Understood. In EU markets, Normalisation is also required. Remove specific language characters and some funny characters. Mobile Connect does this. (Huub KPN) + * Do you mean that fuzzy name logic and Normalisation are for Age Verification only, or Match as well? (Toshi KDDI) + * It can apply not only for Age Verification, but also for Match, I think. (Huub KPN) + * In EU market, for Age Verification, it is needed to add some additional attributes like Name and Email, in order to identify User is Contractor. It is understood that Japan does not need them and wants to make them optional. Will propose some proposal based on today’s discussion. (Huub KPN) **AI #13.04 (Huub KPN)** + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + +* README.md should have Age Verification + * An Issue/PR is to be proposed. (AI #12.01) + +## AOB +* **Next meeting: 2024/5/14(Tue) 0900-1000 CEST.** +* According to the meeting cycle, the next meeting would be held on 2024/4/30(Tue), but Gilles Orange and Toshi KDDI will not be available on that date, meaning two of the three Codeowners will be unavailable, so Toshi proposed to skip the meeting on that day, adding that day (and the week) will be a Japanese holiday (week). The proposal was agreed. +* It was also agreed that GitHub discussion should continue, irrespective of the skip of the regular meeting. +* It was noted that KnowYourCustomer SP regular calls will be held on Zoom platform from the next meeting on 2024/5/14. + +## Action Items +* **AI#13.01**: Toshi will move remaining discussions in Issue #18 to a new Issue to be created for V0.2.0. [Toshi] +* **AI#13.02**: Toshi will move remaining discussions in Issue #22 to a new Issue to be created for V0.2.0. [Toshi] +* **AI#13.03**: Toshi will create Issues for each of the outstanding items listed in Issue #65. [Toshi] +* **AI#13.04**: Huub will share his Age Verification proposal based on discussions made during today’s meeting, with members as a GitHub comment. [Huub] +* **All other remaining AIs** + +[END] + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14.md new file mode 100644 index 0000000000000000000000000000000000000000..ac7c0787d090a042d708efbc37cfc4b0aafc1ba0 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-14.md @@ -0,0 +1,124 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-05-14 + +* Tuesday, May 14th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-04-16 draft; [PR #78](https://github.com/camaraproject/KnowYourCustomer/pull/78), created on April 26th. ->No comments and approved. +* Uploading the meeting 2024-04-16 material -> [PR #76](https://github.com/camaraproject/KnowYourCustomer/pull/76), has been approved and merged. +* Actions: + * Closed: AI #12.01, #13.04 + * Kept open: AI #06.06, #08.01, #08.02, #09.01, #11.01, #12.01, #13.01, #13.02, #13.03 +* Telefonica Fernando commented that he would like to discuss Match v0.1.1 which he had proposed. It was agreed to cover this topic during Match v0.1.0 agenda later. + +## Review Issues & PRs + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * Remaining discussions will be moved to a new issue for v0.2.0. AI #13.01 (Toshi) is still open. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * Remaining discussions can be moved to a new issue for v0.2.0. AI #13.02 (Toshi) is still open. + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * Need to check if this can be merged or should be closed without being merged, as PR #61 was merged. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79))
                                                PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion + * Issue #79 and PR #80 were proposed by Telefonica. In KYC-Match v0.1.0, the example of 'country' attribute is "Japan" (name of country), but Telefonica would like to change it to one of Alpha-2 country codes. Device Status API (Roaming Status) uses Alpha-2 country codes, and Telefonica is implementing KYC-Match API with Alpha-2 country codes. (Telefonica Fernando) + * Fine with Orange. (Orange Gilles) + * May I suggest changing the attribute to 'countryCode' or something? (KDDI Toshi) + * Device Status API uses 'countryCode' attribute for MCC, so Telefonica would suggest using 'country' attribute to avoid potential confusion. Proposal is just to modify the example and not to touch the core v0.1.0 specification. (Telefonica Fernando) + * Fine with Orange. Scrutiny of country-related attributes should be addressed in v0.2.0 discussion. Orange thinks of using TM Forum format for that. (Orange Gilles) + * Agree to revisit this topic in v0.2.0 discussion. For example, Device Status API uses 'countryName' for Alpha-2 codes, and OIDF/OIDC specficications use 'countryCode' for Alpha-2 codes. (KDDI Toshi) + * As both Telefonica and Orange are implementing the Match v0.1.0, this matter should be concluded quickly. (Orange Gilles, Telefonica Fernando) + * It seems it could be agreed that KYC-Match v0.1.0 uses 'country' attribute for Alpha-2 codes and includes an example of Alpha-2 code. However, taking it into account that some members are absent, we could accept any comments within 24 hours if any. (KDDI Toshi) + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39))
                                                PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this Issue will be broken down to Issues for each item. (AI #13.03) + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + + * Ongoing discussion + * How to write address, how to separate address to several fields, are different for the Netherlands, Spain, and Japan. It is difficult. Continue discussion. + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Ongoing discussion + * The Netherlands has a unique way to manage First/Family names. If it is not used, Match rate will worsen. (KPN Huub) + * Telefonica would prefer small number of Attributes in the Match API. (Telefonica Fernando) + * Continue discussion. + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * It seems we have almost completed our discussion on the point, so, now we need to clarify which items are mandatory and which items are optional. (Toshi KDDI) + * From KDDI point of view, Match scoring is not needed. (Toshi KDDI) + * Telefonica will discuss internally on whether Match scoring is needed or not. (Telefonica Fernando) + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. + +### Overall +* Issue #75 Select API for CAMARA Meta-Release September #75 ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing + * This issue will be discussed in the next meeting. + +## AOB +* **Next meeting: 2024/5/28(Tue) 0900-1000 CEST.** + +## Action Items +* **All remaining AIs** + +[END] + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28.md new file mode 100644 index 0000000000000000000000000000000000000000..80b5e362656057dacb2d4bb7ce70ec0906a24fe8 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-05-28.md @@ -0,0 +1,160 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-05-28 + +* Tuesday, May 28th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Axel Nennker, DT +* Clara Serrano, Telefonica +* Jorge Garcia Hospital, Telefonica + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-05-14 draft; [PR #84](https://github.com/camaraproject/KnowYourCustomer/pull/84), created on May 22nd. ->No comments and approved. +* Uploading the meeting 2024-05-14 material; [PR #83](https://github.com/camaraproject/KnowYourCustomer/pull/783), created on May 21st ->No comments and approved. +* Actions: + * Closed: AI #08.01, #13.01, #13.03 + * Kept open: AI #06.06, #08.02, #09.01, #11.01, #13.02 + * Closure of AI #13.01 was confirmed in the related agenda later. + * AI #08.02, #09.01 and #11.01 are thought to be closed. To be checked by next meeting. + +* In relation to AI #08.02, Telefonica Clara shared their view that for Age Verification API, attributes other than Age should be made completely optional, because it may result in application developer’s confusion between Age Verification API and KYC Match API if Age Verification API’s request body has additional attributes e.g. name and email address. KDDI Toshi suggested to discuss this topic in the later Age Verification agenda as the moderator, and, from KDDI perspective, agreed with Telefonica’s view. + +## Review Issues & PRs + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing + * Need to fill in all the necessary items on the release-management template which exists in the KYC-SP’s wiki page. This is one of the steps required for the meta-release. (DT Axel) ->Will study to fill in. (KDDI Toshi) + +* Issue #92 Tenure API to be handled in KYC-SP regular meeting and ML ([Issue #92](https://github.com/camaraproject/KnowYourCustomer/issues/92)) + * Discussion ongoing + * There was no comment. Agreed that Tenure API will use KYC-SP regular meetings and KYC-SP ML + +* Match scoring enhancement was proposed through API Backlog API Backlog ([Issue #45](https://github.com/camaraproject/APIBacklog/issues/45) / ([PR #46](https://github.com/camaraproject/APIBacklog/pull/46) + * Discussion ongoing + * Toshi explained our situation that we have an issue for that, and that we are discussing it. Toshi understand we continue our discussion, taking the proposed template into consideration. Toshi pointed out that KYC Match API (enhanced or whatever it is called) should work without Scoring as some markets/operators/API users do not need Scoring, and that was endorsed by API Backlog WG. + * Related to Issue #85 + * Telefonica Clara commented that backward compatibility is required, as Telefonica has implemented KYC-Match v0.1.0. KDDI Toshi seconded that. + * Continue discussion on Issue #85. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * New item. Asked what members think? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) + * KDDI Toshi commented that his understand was that this API is related to Credit Scoring and Credit Scoring does not have much to do with KYC information. Taking KYC-SP’s workload (many APIs), he feels it is difficult for KYC-SP to include Telco Scoring API. + * Telefonica Jorge Garcia commented that Telco Scoring API has much to do with KYC, as it would use the same data/information for Scoring. + * Continue discussion. + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * It is understood that the remaining topics are covered in new Issue #87, so, we are going to close this issue. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue, but it is to be confirmed if this issue can be closed. + * Stefano's comment is expected. As Stefano is absent, KDDI Toshi will contact Stefano. **AI #15.01 (Toshi)** + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * This PR will be closed without being merged, as PR #61 has already been merged. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79))
                                                PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion + * Regarding Issue #79, Telefonica Fernando would like to confirm if this can be agreed on. + * KDDI Toshi replied that, as commented in Issue #79, KDDI could agree with this proposal on condition that country related parameters will be revisited for the next version. + * As Issue #79 has been agreed, we can move on to validate PR #80. KDDI Toshi sudggested to have PR #80 include YAML modification for Issue #82. + * Telefonica Fernando, who is the owner of PR #80, agreed. **AI #15.02 (Fernando)** + +* Issue #82 Abbreviation "OB" in parameter description ([Issue #82](https://github.com/camaraproject/KnowYourCustomer/issues/82)) + * Ongoing discussion: It is understood that the proposal can be agreed upon. + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + * There have been some discussions on GitHub recently, but, as Huub is absent today, we cannot check what the discussions look like. + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing + * Telefonica Clara commented that, as for Age Verification API, Telefonica does not think additional attributes are necessary to check and score how different the end user seems from the contract owner, and that, if these attributes are added, they should be optional attributes and the API should work without these optional attributes and scoring function. Telefonica Clara is requested to input the comments into GitHub Issue. **AI #15.03 (Clara)** + * After seconding Telefonica’s comments, KDDI Toshi asked Orange Gilles to summarise the current conclusions of the Issue #46 discussion. Gilles agreed. **AI #15.04 (Gilles)** + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. +## AOB +* **Next meeting: 2024/6/11(Tue) 0900-1000 CEST, which will include Tenure API agenda.** + +## Action Items +* **AI#15.01**: KDDI Toshi will contact Stefano to see Stefano’s view on closure of Issue #22. [Toshi] +* **AI#15.02**: Telefonica Fernando will proceed with PR #80 for Issue #79 as well as Issue #82. [Fernando] +* **AI#15.03**: Telefonica Clara will write their comments to GitHub Issue #46 regarding Age Verification API’s additional attributes in request body and scoring in response. [Clara] +* **AI#15.04**: Orange Gilles will summarise the current conclusions of the Issue #46 discussion. [Gilles] +* **All remaining AIs** + +[END] + diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11.md new file mode 100644 index 0000000000000000000000000000000000000000..22be6ae15ccdef2e484fc842f00234448d7de520 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-11.md @@ -0,0 +1,227 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-06-11 + +* Tuesday, June 11th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica +* Jorge Garcia Hospital, Telefonica +* Kevin Scarr, Vodafone +* Ola Ajibola, GSMA + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* MOM 2024-05-28 draft; [PR #94](https://github.com/camaraproject/KnowYourCustomer/pull/94), created on June 1st. ->No comments and approved. +* Uploading the meeting 2024-05-28 material; [PR #93](https://github.com/camaraproject/KnowYourCustomer/pull/93), created on May 28th ->No comments and approved. +* Actions: + * Closed: AI #08.02, #13.01, #15.02, #15.04 + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + + +## Review Issues & PRs + +### New +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th; Discussion ongoing. + * For KYC Match v0.2.0. + * Huub KPN explained his proposal, followed by some discussion. + * Huub KPN: Mobile connect KYC match has this feature, Netherland has this and very useful. Contracts are anonymous, so customer types are important. Prepaid users have to be careful to check identity through other means. What have been done in NL was to match minimum data. But discussion should be open for anti-fraud cases and so on. + * Huub KPN: Customer can check the data or at least get confirmation that it is prepaid. + * ?: No optional feature? MC spec has optional feature? + * Huub KPN: in MC, this spec is optional. In CAMARA, you should make it optional too. Some country is not interested, you might not want to share this information. In the EU market, there are obligation to identify customer irrespective of subscription type, but in NL very useful. + * Jorge TEF: Tenure API is also suggested. Is this the match, so data is provided from customer? + * Huub KPN: They normally check the identity of the user, everything to do with the use case of verifying the identity of a customer, Tenure is different, but can also help specify prepaid or postpaid + * Jorge TEF: Limit optionality of the API, so separate API is good. + * Huub KPN: there are some attributes that can’t be provided, at least add to KYC match the same as MC. + * Clara TEF: + * Huub KPN: Reliability of SIM card, etc. + * Clara TEF: What are the use cases of Tenure? + * Hubb KPN: simply want to know somebody is reliable, put data to a kind of risk engine. + * Clara KPN: independent from match. + Huub KPN: can be used for multi-factor authentication. Banks who check passports are less likely interested in match but more in Tenure. + Clara TEF: In Telefonica we know MC has this feature. Match is true/false while prepaid/pospaid/business is raw data. + Huub KPN: in enterprise police can find out later, so prepaid and business are different. That is a value I want to provide. + + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th; Discussion ongoing. + * For KYC Match v0.2.0. + * Gilles Orange explained his proposal, followed by some discussion. + * Gilles Orange: One enumeration for all attributes. + * Toshi KDDI: will ask Gilles for explanation offline. It is for next version? -> Gilles Orange: Yes. + * Clara TEF: is this for version2? -> Gilles Orange: Yes. + * Gilles Orange: all attributes provide at least enumeration, developer of API find it difficult unless common enumeration. I’ll try to propose implementation of swagger. + * Kevin Carr VDF: are you trying to declare one common enum, instead of enum under each attribute? -> Gilles Orange: Yes. + + +* Issue #97 update and review CODEOWNERS and MAINTAINERS.md file (Hrebert DT) ([Issue #97](https://github.com/camaraproject/KnowYourCustomer/issues/97)) +* PR #98 97 update and review codeowners and maintainersmd file (Hrebert DT) ([PR #98](https://github.com/camaraproject/KnowYourCustomer/pull/98)) + * For General/Admin. To follow Governance Issue #134; modify the codeowners file and add GitHub user IDs to the maintainers.md file + * Opened on June 10th, and **Approved already**. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Discussion ongoing; no new comments + * Toshi commented that this is important issue for our Fall24 Meta-release and this will be discussed in the next meeting and later meetings. + * In Issue #85 discussion later, there was some discussion on Issue #75: Toshi KDDI commented that we do not have much time so he is thinking of making Match/Fill-in v0.1.x our Meta-release candidate. + * Jorge TEF: Meta-release should be s table. If some operators have already deployed, it would be so much better. So, try to add as much feature as possible. + * Toshi KDDI: Let’s discuss Meta-release in Issue #75. Did you Jorge suggest adding Match Scoring? + * Jorge TEF: Yes. + +* Issue #92 Tenure API to be handled in KYC-SP regular meeting and ML ([Issue #92](https://github.com/camaraproject/KnowYourCustomer/issues/92)) + * **To be closed**; Tenure API is now handled as part of KnowYourCustomer API family, as TSC decided. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) ) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) ) + * Ongoing in API Backlog WG + + +### Match/Fill-in v0.1.0 – released version + +* Issue #18 KYC Match – Compare specifications ([Issue #18](https://github.com/camaraproject/KnowYourCustomer/issues/18)) + * **Closed** + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. Can this issue be closed? + +* PR #57 Create CHANGELOG.MD ([PR #57](https://github.com/camaraproject/KnowYourCustomer/pull/57)) + * **Closed without being merged**, as already merged PR #61 covered the same issue. + +* Issue #79 Small release v0.1.1 to fix country example ([Issue #79](https://github.com/camaraproject/KnowYourCustomer/issues/79)) + * **Closed** as completed. +* PR #80 Update description and example of country property to alpha-2 ([PR #80](https://github.com/camaraproject/KnowYourCustomer/pull/80)) + * Ongoing discussion – let's proceed with this RP including Issue #82. + * -> PR modified to cover Issue #82, and then **approved and merged** (for both Match and Fill-in) +* Issue #82 Abbreviation "OB" in parameter description ([Issue #82](https://github.com/camaraproject/KnowYourCustomer/issues/82)) + * **Closed** as completed. + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + * Clara Telefonica commented, followed by some discussion: + * Clara TEF: Mostly acceptable proposal. Telefonica has already implemented this v0.1, so need backward compatibility. Telefonica would here propose not to enforce additional attribute for score, not to change attributes or objects, thus Scoring will not impact existing implementation. Otherwise fine. + * Kevin Carr VDF: Agree. Straightforward for developers to use. + * Gilles Orange: Understand that backward compatibility is strongly needed. + * Toshi KDDI: KDDI’s information is close to v0.1, so KDDI has the same position. + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + * Axel DT commented. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing; Gille's summary appreciated. + * Toshi KDDI commented "is it going to be Meta release? Almost ready for PR discussion?", after which there was some discussion: + * Clara TEF: just mentioning additional attributes in order to validate user, our objective. We only have data birthdate of contract owner, which is reality. We would like to have this info for all user, ambition, not reality. Something we may be able to have in future. Having these attributes mandatory will be in future. + * Huub KPN: one suggestion, we can make it entirely optional. Reflect score on the reliability of the data. We analyzed 30% of the end user are not contract owner, so with no data, we probably return 70%, it is not very reliable. + * Clara TEF: same, even higher. We don’t have all data, even Legal asked us to filter some data. + * Huub KPN: you can also provide very low score, in case if legal says. + * Clara TEF: + * Huub KPN: for example, if only family name is provided, reliability is now 70% to 85%. That’s how you can play with aggregate score, still useful for some use cases, and not mandating any attributes. + * Huub KPN: additional attributes can be optional. + * Clara TEF: I will provide comments to the issue. + * Toshi KDDI: we have enough discussion for ver0.1 on validating user/contact owner. Any additional feature? Let’s wait for Telefonica comments, and then move on to PR discussion. + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* Discussion not yet started, so skipped today. + * Clara Telefonica made a question, followed by some discussion: + * Clara TEF: Question. This API is not to give how long this customer has been a customer of this operator. In some comments, mentioning contract, MSISDN has been assigned to that user, then what exactly does operator have to check data? How long the customer has been in place? It is understood that UK has this API. + * Kevin Carr VDF: it is checking how long this number has been managed, MSISDN has been used, when that number joined to that network. Recycle is another API. + * Hubb KPN: need to be very clear about it, contract to end user? If contract is changed from business to personal to keep that number after leaving the company? + * Clara TEF: if new carrier, then zero? + * Huub KPN: if same carrier, Telefonica, do you reset? That is question we need to answer. + * Toshi KDDI: Details should be discussed anyway. + * Huub KPN: will comment. + + +## AOB +* **Next meeting: 2024/6/25(Tue) 0900-1000 CEST** + +## Action Items +* **No additional AIs from meeting #16** +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25.md new file mode 100644 index 0000000000000000000000000000000000000000..4dcd9c22566c62c870bd3e68c07f6b86cf9a1236 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-06-25.md @@ -0,0 +1,210 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-06-25 + +* Tuesday, June 25th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Fernando Prado Cabrillo, Telefonica +* Gilles Renoux, Orange +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, Telefonica +* Kevin Scarr, Vodafone +* Ola Ajibola, GSMA + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-06-11 draft**; [PR #102](https://github.com/camaraproject/KnowYourCustomer/pull/102), created on June 20th. ->**[06/25]** No comments and approved. To be merged after the meeting. +* **Uploading the meeting 2024-06-11 material**; [PR #99](https://github.com/camaraproject/KnowYourCustomer/pull/99), created on June 11th ->Merged and document uploaded already. +* Actions: + * Closed: None + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + + +## Review Issues & PRs + +### New +* **Issue #100 Release v0.1.1 (Fernando TEF) [Merged]** ([PR #100](https://github.com/camaraproject/KnowYourCustomer/pull/100)) + * Opened on June 13thh; approved and merged + * Create release branch for KYC Match/Fill-in v0.1.1 and include CHANGLOG.md. (The approved PR #80 has already created v0.1.1 YAML.) + * **[06/25]** v0.1.1 is only for minor updates including modification of country field example, and v0.1.1 content itself had been updated by PR #80. This PR #100 is just for version number change and Changelog update. + +* **Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA)** ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * **[06/25]** Ola GSMA: At least any one property must be included in the request body? + * ->Toshi KDDI: the request body needs at least one property, which will be checked with the MNO's data. phoneNumber, i.e. identity, is also needed as mandatory, isn't it? + * ->Fernando TEF) phoneNumber could be retrieved from Access Token, so, at least one property must be included, in addition to phoneNumber. + * ->Fernando TEF) That will be documented in the next update. + * ->Toshi KDDI) OK. Toshi will write the comment to GitHub Issue #101. **AI#17.01 (Toshi)** + +* **PR #103 Align yaml with commonalities v0.3 (Fernando TEF)** ([PR #103](https://github.com/camaraproject/KnowYourCustomer/pull/103)) + * Opened on June 20th; Discussion ongoing + * For KYC Match/Fill-in v0.1.1? + * Align with commonalities v0.3. How about v0.4? + * **[06/25]** **Agreed, as aliment with the Commonalities items is mandatory for Meta-release.** + * Toshi KDDI: It is understood that v0.4 is coming separatly. Correct? ->Fernande TEF: Correct. v0.4 is mandatory for Fall24 Meta-release. + +* **PR #104 Include score functionality proposal (Fernando TEF)** ([PR #104](https://github.com/camaraproject/KnowYourCustomer/pull/104)) + * Opened on June 20th ; Discussion ongoing. For Match v0.2.0. + * To fix ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85) ([KYC Match] Scoring) and ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) (Create a common enum for attributeMatch result) + * **[06/25]** Clara TEF: Telefoncia's YAML proposal. Comments are welcome. This PR includes the above two issues. + * ->Toshi KDDI: Need some time to check the yaml. + * Toshi KDDI: One comment is, as commented in Issue #85, that scoring algorithm should not be mandatory, because there may be more suitable algorithm existing for each country and each language. + * ->TEF: If algorithm is different from countries and languages, the same request may receive different scoring results, which will be an issue. + * ->Kevin Scarr VDF: Jaro-Winkler algorithm has not been used for other languages than European langages. Send link to a website to Toshi. + * Here is the link to the security website that has Jaro-Winkler already implemented. + * https://asecuritysite.com/hashsim/simstring + * Toshi KDDI: In the first place, do we need to specify this kind of algorithm in the API specification? + * ->TEF: It is needed for Developers' understanding. + * ->Toshi KDDI: Then, how about making Jaro-Winkler algorithm as recommendation or as guideline for European language or Europe countries, but keeping algorithm TBD for other languages and countries? + * ->Kevin Scarr VDF) How about writing this sentence in the specification? Proposed: "Unless otherwise captured in the specification, score will use the Jaro-Winkler distance algorithm for all countries." + * ->Toshi KDD: Sounds agreeable. + * ->Clara TEF: Please try Jaro-Winkler algorithm with KDDI's data to find if it works for Japanese language. + * ->Toshi KDDI: I am no quite sure if we can do that, as we do not provide Match Scoring now, but I will discuss internally about trying it. **AI #17.01 (Toshi)** + * Gilles Orange: Orange proposed another endpoint for Match Scoring. + * ->TEF: It is better to have only one endpoint for KYC Match. + * TEF: Telefonica wants to include Match Scoring in Fall24 Meta-release. How will we proceed with this proposal? + * ->Toshi KDDI: Taking Meta-release schedule into account, I understand we have to proceed rapidly. ** Keep this discussion open until our next meeting on 9th July, and next meeting is the target to clear issues.** Let's continue discussion on GitHub. + * ->** Agreed. ** + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing; There were comments to propose KYC Match v0.2 with Scoring + * Thoughts: + * KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)? + * KYC Fill-in v0.1 (initial)? + *Age Verification v0.1 (initial)? + * **[06/25]** Toshi KDDI: Please comment to Issue #75, if any. + +* API Backlog 2024/05/23 Telco Scoring API to be handled in KYC-SP regular meetings? + * Telco Scoring API proposal: API Backlog ([Issue #41](https://github.com/camaraproject/APIBacklog/issues/41) ) / ([PR #42](https://github.com/camaraproject/APIBacklog/pull/42) ) + * Ongoing in API Backlog WG + * **In API Backlog June 13th, Jorge TEF and Toshi KDDI agreed that Telco Scoring API does not fit with KYC-SP. ->Telco Scoring API will not be a KYC Family API. Any objection?** + * **[06/25]** Toshi KDDI: Please send an email or contact to Toshi by next API Backlog WG meeting on June 27th, if you have any comment. **AI#17.02 (All)** + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing; Gille's summary appreciated. + * **[06/25]** Toshi KDDI: commented in Issue #46. If age verification true/false is needed and scoring is not needed, what will be the mandatory parameters? + * ->Gilles Orange: Age only. phoneNumber is optional. + * Toshi KDDI: It is understood that Age Verification v0.1.0 is candidate for Fall24 Meta-release. But, which should be prioritised, Age Verification or Match Scoring? + * ->Clara TEF: Match Scoring should be priortised, though it is not meant to stop Age Verification. + * ->Toshi KDDI: If other members agree with it, from KYC-SP point of view, it is OK. But Age Verification API is a GSMA Drop #3 API and from GSMA point of view, it is expected to be completed as early as possible. From KDDI side, Age Verification is an important one and early completion is expected. + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Created for AI #12.01. Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + +### Tenure v0.1.0 + +* Discussion not yet started, so skipped today. + +## AOB +* **Next meeting: 2024/7/9(Tue) 0900-1000 CEST** + +* **Planned Meetings:** toward Fall24 Meta-release, we plan to keep the cadence. + * #19 July 23rd, + * #20 August 6th, + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + +## Action Items +* **No additional AIs from meeting #16** +* **AI#17.01**: Toshi KDDI will write the comment to GitHub Issue #101 based on the discussion. [Toshi] +* **AI#17.02**: All is requested to send an email or contact to Toshi by next API Backlog WG meeting on June 27th, if you have any comment to the API Backlog's current conclusion that Telco Scoring API will not be a KYC Family API. [All] +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09.md new file mode 100644 index 0000000000000000000000000000000000000000..7346cd5fd6a823dbaf21bfcb12c439e150956a53 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-09.md @@ -0,0 +1,190 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-07-09 + +* Tuesday, July 9th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Surajj Jaggernath, Vodacome +* Kosuke Koiwai, KDDI +* Clara Serrano, TEF +* Jorge Garcia Hospital, TEF +* Kevin Scarr, Vodafone + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-06-25 draft**; [PR #106](https://github.com/camaraproject/KnowYourCustomer/pull/106), created on July 2nd. ->**[July 9th]** No comments and approved. To be merged after the meeting. +* **Uploading the meeting 2024-06-25 material**; [PR #105](https://github.com/camaraproject/KnowYourCustomer/pull/105), created on June 27th ->Merged and document uploaded already. +* Actions: + * Closed: AI #17.01, #17.02 + * Kept open: AI #06.06, #09.01, #11.01, #13.02, #15.01, #15.03 + * [July 9th] Agreed to close AI #09.01, #11.01 + +## Review Issues & PRs + +### New +* No new Issues/PRs except last meeting MoM and Agenda document. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * To be confirmed + * KYC Match v0.2 (v0.1 initial + v0.2 adds scoring) + * KYC Fill-in v0.1 (initial) + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **[July 9th]** No specific comment was raised during the meeting. The above was confirmed as current KYC-SP’s target for Fall24 Meta-release. + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* **Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA)** ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + * **[July 9th]** Clara and Jorge Telefonica ar ok with Toshi's comment on GitHub, but it is better to wait for Gilles and Fernando's check. Toshi will reach out to them. **AI#18.01 (Toshi)** + +* **PR #103 Align yaml with commonalities v0.3 (Fernando TEF)** ([PR #103](https://github.com/camaraproject/KnowYourCustomer/pull/103)) + * Opened on June 20th; Discussion ongoing + * For KYC Match/Fill-in v0.1.1? + * Discussed in Meeting 2024/06/25. **If no further comment, this will be approved and merged.** + * **[July 9th]** Approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. **AI#18.02 (Toshi)** + + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* **PR #104 Include score functionality proposal (Fernando TEF)** ([PR #104](https://github.com/camaraproject/KnowYourCustomer/pull/104)) + * Opened on June 20th ; Discussion ongoing. + * For Match v0.2.0. + * To fix ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85) ([KYC Match] Scoring) and ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) (Create a common enum for attributeMatch result) + * **[July 9th]** Approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. **AI #18.03 (Toshi)** + * Jorge and Clara TEF: as Fernando is on leave, codeowners are requested to merge PR #103 and PR #104. (Toshi will do.) Then, Telefonica will take care of further PRs toward Meta-release. For example, Commonalities v0.4 for Fall24 Meta-release. + * (Related to Issue #75) Toshi showed API readiness checklist on Release Management Wiki page, and shared his view that the following items should be worked on specifically; No.2 Design guidelines from Commonalities applied (v0.4), No.3 Guidelines from ICM applied (v0.2), and No.7 Basic API test cases & documentation. Other items are covered by usual API specification work or not needed as optional. Also, all required items shall be done by M4 August 31st, and release-candidate shall be ready then. + * Jorge TEF: agreed to start the necessary work as a basis, asked by Toshi KDDI. Thank you. + * Jorge TEF: also agreed to enter kyc-fill-in v0.1 into API Release Tracking, asked by Toshi KDDI. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* Toshi's observertion of current situation on Tenure API repo is briefed on page 14 of the meeting material. +* **[July 9th]**: It seems discussion not yet started, so skipped today. +* Clara TEF: TEF would like to prioritize Tenure API. +* Toshi KDDI: Noted. But, in API Backlog WG, it is being discussed how to proceed with these three APIs which have some common aspects, though start of Tenure API work in KYC SP has been approved by TSC. In addition, Tenure API lead is not identified. So, it is likely that eventually Tenure API will go on track. +* Kevin Scarr VDF: will contact Vodafone's Tenure member (Saker) to find out Tenure lead. **AI #18.04 (Kevin Scarr VDF)** + + +## AOB +* **Next meeting: 2024/July/23rd(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #20 August 6th, + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + + +## Action Items + +* **AI#18.01**: Clara and Jorge Telefonica are ok with Toshi's comment on GitHub, but it is better to wait for Gilles and Fernando's check. Toshi will reach out to them. [Toshi KDDI] +* **AI#18.02**: PR #103 Align yaml with commonalities v0.3 was approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave. [Toshi KDDI] +* **AI#18.03**: PR #104 Include score functionality proposal was approved during the meeting. Toshi is to merge the PR, as Fernando TEF is on leave.[Toshi KDDI] +* **AI#18.04**: Kevin Scarr VDF will contact Vodafone's Tenure member (Saker) to find out Tenure lead. [Kevin Scarr VDF] +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23.md new file mode 100644 index 0000000000000000000000000000000000000000..d9b6f46695ab1f8fd1c394558cd82c0d1b5930a0 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-07-23.md @@ -0,0 +1,213 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-07-23 + +* Tuesday, July 23rd, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Tet (Tetsuya) Chiba, KDDI +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Kiyoto Shinomura, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Clara Serrano, TEF +* Jorge Garcia Hospital, TEF +* Kevin Scarr, Vodafone +* Luis Lopez, Vodafone +* George, DT + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-07-09 draft**; [PR #113](https://github.com/camaraproject/KnowYourCustomer/pull/113), created on July 12th.
                                                ->**[July 23rd]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-07-09 material**; [PR #110](https://github.com/camaraproject/KnowYourCustomer/pull/110), created on July 10th
                                                ->Merged and document uploaded already. + +* Actions: + * Closed: AI #18.02, #18.03 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, + * **[July 23rd]** Agreed to close AI #18.04, as Kevin Scarr VDF confirmedt that Luis Lopez VDF is the Tenure API lead, adding Kevin Scarr will also join the Tenure API discussion as a technical staff. + +## Review Issues & PRs + +### New + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) + * Opened on 2024/07/22. For both Match and Fill-in. + * **[July 23rd]** This PR is for alignment with Commonalities v0.4, and needs to be approved and merged for Meta-release Fall24. + * Together with PR #115 and PR #111, this needs to be approved and merged within this week, in order to meet Meta-release Fall24 M3 deadline.
                                                ->To meet this deadline, **this PR should be reviewed within 48 hours after the meeting ends**. +
                                                -> **All to review the PR #114 by 48 hours after the meeting ends.** **AI #19.01 (All)** + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) + * Opened on 2024/07/22. + * For Match only. Is the same content required for Fill-in? + * **[July 23rd]** This PR proposes to add Device Object-related requirements to the API specification, however, the proposal has not been approved in Commonalities, so, this PR need not be approved and merged for Meta-release Fall24 from the perspective of Commonalities alignment. Commonalities WG is supposed to approve this proposal for Mete-release Spring25, so, we could postpone this proposal till Spring25 as well. + * Jorge TEF: we should decide this to be approved and merged or not, by end of this week, to meet Fall24 Meta-release M3 deadline. +
                                                -> Toshi KDDI: Is it possible for us to make the preliminal decidion by end of this week, and then to correct it by a PR by M4 deadline, if needed? +
                                                -> Jorge TEF: That would not be a simple correction, so, it is not possible. +
                                                -> Toshi KDDI: Understood. Let's open for comments for 48 hours after the meeting ends, and then decide. +
                                                -> **All to review the PR #115 by 48 hours after the meeting ends.** **AI #19.02 (All)** + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) + * Opened on 2024/07/23. + * Corresponding to Issue #104 for Match. + * **[July 23rd]** This PR is to proceed with Fill-in API Fall 24 Mete-release, same as Match v0.2. +
                                                ->Jorge TEF: Version number needs to be changed from v0.1 to v0.1-rc1, as Herbert pointed out. + + +### General +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 – wip + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue Issue #89 ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + * **[July 23rd]** This PR is for creation of Mete-release RC (Release Candidate), and needs to be approved and merged for Meta-release Fall24. + * Together with PR #115 and PR #114, this needs to be approved and merged within this week, in order to meet Meta-release Fall24 M3 deadline. To meet this deadline, **this PR should be reviewed within 48 hours after the meeting ends**. +
                                                -> **All to review the PR #111 by 48 hours after the meeting ends.** **AI #19.03 (All)** + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **[July 23rd]** Jorge TEF: There are two points to be decided today.
                                                (1) MatchScoreResult integer or float,
                                                (2) Scoring provides numbers only, and how to understand numbers is left to developers, assuming Jaro-Winkler algorithm is used. + * **(1) Agreed: interger.**
                                                -> Huub KPN: ok for interger, if it is KYC SP's decision. However, from KPN's experience of Mobile Connect, it may be changed to float in future. + * **(2) Agreed: Scoring provides numbers only.**
                                                ->Huub KPN: KPN is providing Match Scoring, and KPN leaves it (how to understand numbers) to customers (developers, API users), because requirements are different from each customer. KPN provides some supporting documents which are not included in API description. Regarding Normalisation, it should be done locally (by each country / operator), as it is different from countries and langugages. + * Geroge DT: who joined the meeting for the first time, made some questions on Match Scoring, Privacy issues and so on, which were answered by KYC SP members. + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* **[July 23rd]** No discussion on Tenure API, as there was not enough time remaining. +* Clara TEF: TEF would like to focus on Tenure API once KYC Match v0.2 is closed. +* Toshi KDDI: Noted. But it will be contribution driven. KDDI would like to focus on Age Verification and Number Recycling which is new. + + +## AOB +* **Next meeting: 2024/August/6th(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #21 August 20th, + * #22 September 3rd, + * #23 September 17th + * #24 October 1st + +## Action Items + +* **AI#19.01**: All to review the PR #114 by 48 hours after the meeting ends. [All] +* **AI#19.02**: All to review the PR #115 by 48 hours after the meeting ends. [All] +* **AI#19.03**: All to review the PR #111 by 48 hours after the meeting ends. [All] +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06.md new file mode 100644 index 0000000000000000000000000000000000000000..c3631cf84e2ddd655dfa2e79d59d78210a4cbb2e --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-06.md @@ -0,0 +1,297 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-08-06 + +* Tuesday, August 6th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, TEF +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Axel Nennker, DT +* Clara Serrano, TEF +* Ola Ajibola, GSMA +* Luis Lopez, Vodafone +* Kenichi Yamamoto, KDDI [New] +* Guan-Han Ma, Chunghwa Telecom [New] +* Masaharu Hattori, KDDI [New] +* Frank Tsai, Chunghwa Telecom [New] + +Four new contributors and a new company, Chunghwa Telecom (Taiwan), were welcomed. + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-07-23 draft**; [PR #128](https://github.com/camaraproject/KnowYourCustomer/pull/128), created on August 3rd.
                                                ->**[August 6th]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-07-23 material**; [PR #127](https://github.com/camaraproject/KnowYourCustomer/pull/127), created on August 2nd
                                                ->Merged and document uploaded already. + +* Actions: + * Closed: AI #19.01, #19.02, #19.03 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, + + +## Review Issues & PRs + +### General - Meta-release overall status was reviewed first. +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + * **[August 6th]** API Release Trackers were reviewed; [Match](https://wiki.camaraproject.org/display/CAM/kyc-match+v0.2.0), [Fill-in](https://wiki.camaraproject.org/display/CAM/kyc-fill-in+v0.1.1) + * Release Issue was reviewed; [Issue #68](https://github.com/camaraproject/ReleaseManagement/issues/68) KnowYourCustomer r1.1 release review + * Remaining items; Test files should be made available. +
                                                ->Toshi) By when, we have to prepare them? +
                                                ->Rafal)Will check, during the meeting, hopefully. +
                                                ->Fernando) Will take care of Match test file, but not Fill-in test file. +
                                                ->Toshi) Is supposed to take care of Fill-in test file. +
                                                ->Toshi) Asked Fernando if he have started preparing Match test file, considering copying it to create Fill-in test file? +
                                                ->Fernando) replied not yet, but mentioned he has created SIM Swap test files, so he can create Match test file in the same way, and as Match is Initial release, it would be easier. + * **After the meeting**, Rafal emailed Fall24 Meta-release schedule to KYC-SP ML. +
                                                ->According to this, it is understood: + * that we can put 'tbd' for test files in the Readiness Checklist in the meantime + * that we have to prepare test files by M4 deadline, i.e. August 26th. + + + +### New + +* **Issue #117 [KYC Match / KYC Fill-in] givenName appears as giventName in specification examples / Toyeeb GSMA** ([Issue #117](https://github.com/camaraproject/KnowYourCustomer/issues/117)) + * Opened on 2024/07/25. For both Match and Fill-in. + * Corrections: giventName -> givenName, added Scoring response example float -> integer + * Already covered by PR #119, so, **this issue can be closed**. + +* **PR #118 Create API-Readiness-Checklist_kyc-fill-in / Toshi KDDI** ([PR #118](https://github.com/camaraproject/KnowYourCustomer/pull/118)) + * Opened on 2024/07/25. For Fill-in Meta-release. **Approved and merged on 2024/07/26.** + +* **PR #119 Pre release r1.1 for kyc-match + kyc-fill-in + CHANGELOG + README / Fernando TEF** ([PR #119](https://github.com/camaraproject/KnowYourCustomer/pull/119)) + * Opened on 2024/07/26 + * For Fall24 Meta-release candidate creation. Still open. + * KYC Fill-in version changed from v0.1.1 to v0.2.0, according to Herbert’s suggestion. + + +* **Issue #120 [kyc-match]: gender-example in the request is not aligned with the gender-enum / maxl2287** ([Issue #120](https://github.com/camaraproject/KnowYourCustomer/issues/120)) + * Opened on 2024/07/29. + * Gender example modified from Uppercase to lower case. Fixed by [PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121), and **Closed**. + + +* **PR #121 [kyc-match]: Uppercase gender-value in request-example / maxl2287** ([PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121)) + * Opened on 2024/07/29. For Issue #120. Approved and merged on 2024/07/30. + * **[August 6th]** Toshi KDDI) Maxl2287/ Maximilian is not in today, but does anybody know which company Maxl2287/ Maximilian is from? +
                                                ->Rafal DT) DT, development side. + + +* **Discussion #122 What to expect for Hankaku & Zenkaku? / maxl2287** ([Discussion #122](https://github.com/camaraproject/KnowYourCustomer/discussions/122)) + * Opened on 2024/07/31. + * **[August 6th]** Toshi KDDI) has answered to his question. Hope he would be happy. + + +* **PR #123 KYC-Match: IdDocument type / Ramesh SpryFox** ([PR #123](https://github.com/camaraproject/KnowYourCustomer/pull/123)) + * Opened on 2024/08/01. + * **[August 6th]** Toshi KDDI) Fernando, have you looked at this PR? Can this PR be included in Fall24 Meta-release as correction, or is this for next releases as Enhancement? +
                                                ->Fernando TEF) This PR should be for next releases. +
                                                ->Huub KPN) This topic is very complex, so much discussion will be needed. +
                                                ->**Agreed to work on this PR for future releases.** +
                                                ->Toshi KDDI) will note as GitHub comment. **AI #20.01 (Toshi KDDI)** + + +* **Issue #124 KYC-Match: Matches the subscriber or phone user data? / Ramesh SpryFox** ([Issue #124](https://github.com/camaraproject/KnowYourCustomer/issues/124)) + * Opened on 2024/08/01. + * Same as Issue #89. + * **[August 6th]** Agreed: To be discussed for next versions. + + +* **Issue #125 Align info.description Auth section with ICM 0.2.0 / Fernando TEF Issue #125** ([Issue #125](https://github.com/camaraproject/KnowYourCustomer/issues/125)) +* **PR #126 Align info.description Auth section with ICM 0.2.0 / Fernando TEF** ([PR #126](https://github.com/camaraproject/KnowYourCustomer/pull/126)) + * Opened on 2024/08/02 + * For Fall24 Meta-release, alignment to ICM v0.2.0, for both Match and Fill-in. + * **[August 6th]** Toshi KDDI) As this is for alignment with ICM v0.2.0, we should approved this. After the meeting, Toshi will approve this straightaway, so, would like Fernando to merge this without Gilles' approval as he is on holiday and the subproject approved this at the meeting anyway. +
                                                ->Fernando TEF) OK. + + +* **Issue #129 Fix images links in Yaml files / Fernando TEF** ([Issue #129](https://github.com/camaraproject/KnowYourCustomer/issues/129)) +* **PR #130 Update flow images links / Fernando TEF** ([PR #130](https://github.com/camaraproject/KnowYourCustomer/pull/130)) + * Opened on 2024/08/05 + * Correction. + * **[August 6th]** Toshi KDDI) he thought it was only for corrections of the links for the flow drawing file, but 'Files Changes' showed Line 13 (not relating to the link) as well. Commented to the PR in GitHub. +
                                                Fernando TEF) There was a correction of a typo. +
                                                Toshi KDDI) Now I found you had replied so in GitHub. Understood. Thank you. +
                                                ->Toshi KDDI) Then, after the meeting, Toshi will approve this straightaway, so, would like Fernando to merge this without Gilles' approval as he is on holiday and the subproject approved this at the meeting anyway. +
                                                ->Fernando TEF) OK. + + + +### Match/Fill-in v0.2.0 – For Fall24 Meta-release + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) + * Opened on 2024/07/22. For both Match and Fill-in. + * **Approved and merged** + + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) + * Opened on 2024/07/22. + * Discussed on 2024/07/23 meeting, and by comments within 48 hours, this PR has been postponed. + * But Fernando has revisited this PR. + * **[August 6th]** This PR is about the way to describe how to handle 'phoneNumber' in API Description, related to 3-legged Access Token. Commonalities' API Design Guidelines have had guide about how to handle Device Object but not yet handle phoneNumber, so, this PR includes text modified for KYC/phoneNumber by Rafal DT and Fernando TEF, based on SIM Swap's description. + * Toshi KDDI) As commented in GitHub PR, I would prefer to postpone it as it is not agreed by Commonalities. +
                                                -> Fernando and Clara TEF) will discuss internally in Telefonica and will comment to GitHub PR within today. +
                                                -> Rafal DT) also will discuss internally in DT by tomorrow morning. +
                                                -> Toshi KDDI) OK. Let's keep this PR open for comments within 24 hours after the meeting closed. +
                                                -> Huub KPN) This is related to API Misuse and Privacy issue in Commonalities. + * **All to re-review the PR #115 by 24 hours after the meeting ends.** **AI #20.02 (All)** + + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) + * Opened on 2024/07/23. + * Corresponding to Issue #104 for Match. + * PR #118 covers this issue, and PR #118 has been merged. + + + +### General - other than Fall24 Meta-release + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + * Conclusion: as in Issue #109 + + + +### Match/Fill-in v0.1.0 – released version +* Release version v0.1.1 completed with some correction. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + +### Match/Fill-in v0.2.0 + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) **Closed** + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) *Merged** + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **Can be closed, as we agreed with 'integer'.** + + +### Age Verification v0.1.0 – wip + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + +### Tenure v0.1.0 + +* **[August 6th]** Clara TEF made a question, and there was some discussion about the question. +* Toshi KDDI) suggested that it would be better to create GitHub issues for recording and openness/transparency purposes. + + +## AOB +* **Next meeting: 2024/August/21st(Tue) 0900-1000 CEST** + +* **Planned Meetings:** as Fall24 Meta-release is approaching, we keep the two week cadence. + * #22 September 3rd, + * #23 September 17th + * #24 October 1st + +## Action Items + +* **AI#20.01**: Toshi will write a comment to GitHub PR that it was agreed that PR #123 would be discussed for future releases. [Toshi] + +* **AI#20.02**: All to re-review the PR #115 by 24 hours after the meeting ends. [All] + +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20.md b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20.md new file mode 100644 index 0000000000000000000000000000000000000000..88a65339ff735e0610dc8e6efa02f5c69b8e72f7 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/MOM-2024-08-20.md @@ -0,0 +1,297 @@ +# CAMARA KnowYourCustomer meeting - MOM-2024-08-20 + +* Tuesday, August 20th, 2024 + + +## Attendees + +* Toshi (Toshiyasu) Wakayama, KDDI +* Fernando Prado Cabrillo, TEF +* Gilles Renoux, Orange +* Huub Appelboom, KPN +* Kazuma Kameyama, KDDI +* Rafal Artych, DT +* Kosuke Koiwai, KDDI +* Jorge Garcia Hospital, TEF +* Ola Ajibola, GSMA +* Luis Lopez, Vodafone +* Masaharu Hattori, KDDI [New] + +KnowYourCustomer minutes: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) + +Meeting documents: [https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/SupportingDocuments) + + +## Agenda +* Review MoM & Actions +* Review Issues & PRs + * New + * General + * KYC Match/ Fill-in v0.1.0 + * KYC Match/ Fill-in v0.2.0 + * Age Verification v0.1.0 + * Tenure v0.1.0 (plan) +* AOB + +The Agenda was approved. + + +## Review MoM & Actions + +* **MOM 2024-08-06 draft**; [PR #132](https://github.com/camaraproject/KnowYourCustomer/pull/132), created on August 13th.
                                                ->**[August 20th]** No comments and approved. To be merged after the meeting. + +* **Uploading the meeting 2024-08-06 material**; [PR #131](https://github.com/camaraproject/KnowYourCustomer/pull/131), created on August 7th
                                                ->Merged and document uploaded already. + +* Actions: + * Closed: AI #20.02 + * Kept open: AI #06.06, #13.02, #15.01, #15.03, #18.01, #20.01 + + +## Review Issues & PRs + +### General - Meta-release overall status was reviewed first. +* Issue #75 Select API for CAMARA Meta-Release September ([Issue #75](https://github.com/camaraproject/KnowYourCustomer/issues/75)) + * Ongoing discussion + * **Target confirmed:** + * **KYC Match v0.2 (v0.1 initial + v0.2 adds scoring)** + * **KYC Fill-in v0.1 (initial)** + * Age Verification v0.1 (initial) -> de-prioritized and not included in Fall24 + * **Release: Initial public release** + * **[August 20th]** + * **Should test files be made available by M4 deadline (2024/08/26)?** +
                                                Yes, but it is unclear how strictly the deadline for test files will be applied, because there are many APIs that have not test files available yet. +
                                                Anyway, it was agreed to try to create test files by the deadline. Issues will be opened first. Fernando TEF for KYC Match, Toshi KDDI for KYC Fill-in. **AI #21.01 (Fernando TEF, Toshi KDDI)** + * **Do we have to create another PR for Release r1.1 or Meta-release, in addition to PR #119 Pre-release r1.1 which has been merged?** +
                                                Yes, Release PR is required. Release PR would have some differences from Pre-release PR; for example, Changelog, Checklist (test files "to be available" to "Yes"), etc. Release PR's deadline is August 26th. + * **after the meeting** Deadline for Release PR is August 26th, but the deadline for test files (and other release items) is August 30th, since Release PR is expected to get ready for approval/merging by August 30th. + + +### New + +* **Issue #133 KYC-match: When provider decides which information to not send - expected response/Output? / Natylee93** ([Issue #133](https://github.com/camaraproject/KnowYourCustomer/issues/133)) + * Opened on 2024/08/14. For Fill-in, not Match? + * **[August 20th]** Toshi has commented his answer for Fill-in. Natylee93's respose is awaited, as Natlee93 was not in, + +* **Issue #134 KYC Match : CountryMatchScore makes no sense / Huub KPN** ([Issue #134](https://github.com/camaraproject/KnowYourCustomer/issues/134)) + * Opened on 2024/08/14. + * For Match, as ‘Country’ has now become ISO 3166-1 alpha-2, countryMatchScore is not needed. +
                                                ->Makes sense. Can this be incorporated into Fall24 meta? + * **[August 20th]** Fernando TEF will open a PR for this Issue, to incorporate this into Meta release. **AI #21.02 (Fernando TEF)** + +* **Issue #135 [KYC Match] Which fields are meant to be used for identification of the mobile phone user? / Toyeeb GSMA** ([Issue #135](https://github.com/camaraproject/KnowYourCustomer/issues/135)) + * Opened on 2024/08/15. + * IdDocument related error. + * **[August 20th]** Fernando TEF will open a PR for this Issue, to incorporate this into Meta release. **AI #21.03 (Fernando TEF)** + + +* **Issue #136 Start using LF Confluence for agenda and minutes / Fernando** ([Issue #136](https://github.com/camaraproject/KnowYourCustomer/issues/136)) + * Opened on 2024/08/19. + * Subproject Management. + * **[August 20th]** Toshi will start using LF Confluence. This has been one of Toshi's actions for a while. After the current Meta-release rush, so probablly from next meeting. Maybe from this meeting's minutes, but unlikely. + + + +### General - other than Fall24 Meta-release **(No update)** + +* Issue #109 Do Tenure API, NumberRecycling API and Shutdown Service Status API fit in KYC Family /KYC SP meeting? ([Issue #109](https://github.com/camaraproject/KnowYourCustomer/issues/109)) + * Ongoing discussion + * Conclusion: as in Issue #109 + + + +### Match/Fill-in v0.1.0 – released version **(No update)** +* Release version v0.1.1 completed with some correction. + +* Issue #22 KYC Match – KYC Match Request / Response attribute suffix ([Issue #22](https://github.com/camaraproject/KnowYourCustomer/issues/22)) + * It seems there is no remaining topic in this Issue. **Can this issue be closed?** + +* Issue #101 [KYC Match] Will there be a minimum number of properties in the request body? (Ola GSMA) ([Issue #101](https://github.com/camaraproject/KnowYourCustomer/issues/101)) + * Opened on June 19th; Discussion ongoing. + * For KYC Match v0.1.1. + * Discussed in Meeting 2024/06/25. GitHub commented on July 4th. **Can this issue be closed?** + + + +### Match/Fill-in v0.2.0 + +* Issue #38 Proposition of design evolution ([Issue #38](https://github.com/camaraproject/KnowYourCustomer/issues/38)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #39 Polymorphism and discriminator for specific requirements ([Issue #39](https://github.com/camaraproject/KnowYourCustomer/issues/39)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #43 Match API Design evolution proposal ([PR #43](https://github.com/camaraproject/KnowYourCustomer/pull/43)) + * Discussion ongoing, together with Issue #39. + +* Issue #47 Data Minimization for Protection Against Misuse of KYC Data ([Issue #47](https://github.com/camaraproject/KnowYourCustomer/issues/47)) + * Discussion ongoing. ->Continue discussion on GitHub + +* Issue #65 KYC Match/Fill-in v0.1.0 leftover issues, new features, functional enhancement for next versions ([Issue #65](https://github.com/camaraproject/KnowYourCustomer/issues/65)) + * Discussion ongoing ->This Issue is listing items for next versions, which were identified at the completion of v0.1.0. + * Items included in this issue have been broken down to Issues for each item, as per AI #13.03. Issue have not been created for some items because of lack of clarity, so Issue #65 is kept open to discuss these remaining items. + +* Issue #66 Country attribute variation ([Issue #66](https://github.com/camaraproject/KnowYourCustomer/issues/66)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #71 Use houseNumber instead of streetNumber ([Issue #71](https://github.com/camaraproject/KnowYourCustomer/issues/71)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #77 Add initials to the attribute list ([Issue #77](https://github.com/camaraproject/KnowYourCustomer/issues/77)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #85 [KYC Match] Scoring ([Issue #85](https://github.com/camaraproject/KnowYourCustomer/issues/85)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #86 [KYC Match] Hash and some additional parameters ([Issue #86](https://github.com/camaraproject/KnowYourCustomer/issues/86)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #87 [KYC Match / KYC Fill-in] Coexistence of aggregated fields and separate fields for Name and Address ([Issue #87](https://github.com/camaraproject/KnowYourCustomer/issues/87)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #88 [KYC Match / KYC Fill-in] ways to handle country/market specific attributes better ([Issue #88](https://github.com/camaraproject/KnowYourCustomer/issues/88)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #89 [KYC Match / KYC Fill-in] The end-user vs contract owner issue ([Issue #89](https://github.com/camaraproject/KnowYourCustomer/issues/89)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #90 [KYC Fill-in] Attributes to be included in the request body? ([Issue #90](https://github.com/camaraproject/KnowYourCustomer/issues/90)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #91 [KYC Match / KYC Fill-in] OpenID Foundation (OIDF) collaboration ([Issue #91](https://github.com/camaraproject/KnowYourCustomer/issues/91)) + * Discussion ongoing ->Continue discussion on GitHub + +* Issue #95 Add postpaid / prepaid / business information to KYC Match (Huub KPN) ([Issue #95](https://github.com/camaraproject/KnowYourCustomer/issues/95)) + * Opened on June 7th ; Discussion ongoing + +* Issue #96 Create a common enum for attributeMatch result (Gilles Orange) ([Issue #96](https://github.com/camaraproject/KnowYourCustomer/issues/96)) + * Opened on June 7th ; Discussion ongoing + +* Issue #107 KYC Match Readiness Checklist (Jorge TEF) ([Issue #107](https://github.com/camaraproject/KnowYourCustomer/issues/107)) **(Closed)** + * Discussion ongoing + +* **PR #111 Create KYC 0.2.0-rc1 (Jorge TEF)** ([PR #111](https://github.com/camaraproject/KnowYourCustomer/pull/111)) **(Merged)** + * Discussion ongoing + * Discussion on MatchScoreResult type integer or float + +* **Issue #112 [KYC Match] MatchScoreResult type integer or float (Rafal DT)** ([Issue #112](https://github.com/camaraproject/KnowYourCustomer/issues/112)) + * Discussion ongoing + * **Can be closed, as we agreed with 'integer'.** + + + +### Match/Fill-in v0.2.0 – For Fall24 Meta-release + +* **PR #114 Alignment of info, servers objects and security scope names (Rafal DT)** ([PR #114](https://github.com/camaraproject/KnowYourCustomer/pull/114)) **(Merged)** + * Opened on 2024/07/22. For both Match and Fill-in. + + +* **PR #115 KYC-Match: Error responses alignment with Commonalities (Rafal DT)** ([PR #115](https://github.com/camaraproject/KnowYourCustomer/pull/115)) **(Open)** + * Opened on 2024/07/22. + * Discussed on 2024/07/23 meeting, and by comments within 48 hours, this PR has been postponed. + * Discussed on 2024/08/06 meeting, and by comments within 24 hours, this PR has been postponed. + * This PR/topic needs to be discussed right after the Fall24 Meta rush. This PR/topic is related to ‘handling of 3-legged token and device object’ topic, which is covered by Commonalities v0.4.0 (for Fall24 Meta), and API misuse topic, which is being discussed in Commonalities. + + +* **Issue #116 KYC Fill-in Readiness Checklist (Toshi KDDI)** ([Issue #116](https://github.com/camaraproject/KnowYourCustomer/issues/116)) **(Closed on 2024/08/19)** + * Opened on 2024/07/23. + * PR #118 covers this issue, and PR #118 has been merged. + + +* **Issue #117 [KYC Match / KYC Fill-in] givenName appears as giventName in specification examples / Toyeeb GSMA** ([Issue #117](https://github.com/camaraproject/KnowYourCustomer/issues/117)) **(Closed on 2024/08/19)** + * Opened on 2024/07/25. For both Match and Fill-in. + ** Already covered by PR #119, so, **this issue can be closed**. + + +* **PR #118 Create API-Readiness-Checklist_kyc-fill-in / Toshi KDDI** ([PR #118](https://github.com/camaraproject/KnowYourCustomer/pull/118)) **(Merged)** + * Opened on 2024/07/25. For Fill-in Meta-release. Approved and merged on 2024/07/26. + + +* **PR #119 Pre release r1.1 for kyc-match + kyc-fill-in + CHANGELOG + README / Fernando TEF** ([PR #119](https://github.com/camaraproject/KnowYourCustomer/pull/119)) **(Merged)** + * Opened on 2024/07/26 + * For Fall24 Meta-release candidate creation. Still open. + * KYC Fill-in version changed from v0.1.1 to v0.2.0, according to Herbert’s suggestion. + + +* **Issue #120 [kyc-match]: gender-example in the request is not aligned with the gender-enum / maxl2287** ([Issue #120](https://github.com/camaraproject/KnowYourCustomer/issues/120)) **(Closed)** + * Opened on 2024/07/29. + * Gender example modified from Uppercase to lower case. Fixed by [PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121), and **Closed**. + + +* **PR #121 [kyc-match]: Uppercase gender-value in request-example / maxl2287** ([PR #121](https://github.com/camaraproject/KnowYourCustomer/pull/121)) **(Merged)** + * Opened on 2024/07/29. For Issue #120. Approved and merged on 2024/07/30. + +* **Discussion #122 What to expect for Hankaku & Zenkaku? / maxl2287** ([Discussion #122](https://github.com/camaraproject/KnowYourCustomer/discussions/122)) **(Answered)** + * Opened on 2024/07/31. + + +* **PR #123 KYC-Match: IdDocument type / Ramesh SpryFox** ([PR #123](https://github.com/camaraproject/KnowYourCustomer/pull/123)) **(Enhancement)** + * Opened on 2024/08/01. + * Related to IDDocument type. Correction, or Enhancement/ + * Meeting on 2024/08/06 agreed that this issue is to be discussed for future versions. + * **[August 20th]** On GitHub, Huub and Axel replied, and Ramesh was satisfied. There was a question what responses are expected under the current spec. +
                                                Toshi confirmed at the meeting that true, false, not available. + + +* **Issue #124 KYC-Match: Matches the subscriber or phone user data? / Ramesh SpryFox** ([Issue #124](https://github.com/camaraproject/KnowYourCustomer/issues/124)) **(Enhancement)** + * Opened on 2024/08/01. + * Same as Issue #89. + * Meeting on 2024/08/06 agreed that this issue is to be discussed for future versions. + + +* **Issue #125 Align info.description Auth section with ICM 0.2.0 / Fernando TEF Issue #125** ([Issue #125](https://github.com/camaraproject/KnowYourCustomer/issues/125)) **(Closed)** +* **PR #126 Align info.description Auth section with ICM 0.2.0 / Fernando TEF** ([PR #126](https://github.com/camaraproject/KnowYourCustomer/pull/126)) **(Merged)** + * Opened on 2024/08/02 + * For Fall24 Meta-release, alignment to ICM v0.2.0, for both Match and Fill-in. + + +* **Issue #129 Fix images links in Yaml files / Fernando TEF** ([Issue #129](https://github.com/camaraproject/KnowYourCustomer/issues/129)) **(Closed)** +* **PR #130 Update flow images links / Fernando TEF** ([PR #130](https://github.com/camaraproject/KnowYourCustomer/pull/130)) **(Merged)** + * Opened on 2024/08/05 + * Correction. + + + +### Age Verification v0.1.0 – wip **(No update)** + +* Issue #46 Creation of a Pull Request for Age Verification API ([Issue #46](https://github.com/camaraproject/KnowYourCustomer/issues/46)) + * Discussion ongoing. ->Continue discussion on GitHub + +* PR #50 Initial contribution of Age_Verification.yaml ([PR #50](https://github.com/camaraproject/KnowYourCustomer/pull/50)) + * Discussion ongoing. ->Continue discussion on GitHub + * Draft User Story has been proposed, but it is still to be modified depending on ongoing discussions, so, the draft user story cannot be approved at the moment. + +* Issue #81 Add Age Verification to KnowYourrCustomer SP’s Scope in README ([Issue #81](https://github.com/camaraproject/KnowYourCustomer/issues/81)) + * Discussion ongoing. + * A text proposed in the Issue. A PR will be created if the proposed text is OK. ->Will need to be modified in line with Issue #46 / PR #50. + + + +### Tenure v0.1.0 + +* **[August 20th]** Luis Lopez VDF explained: there is not much progress, as members' return from summer holiday is awaited. + + + +## AOB +* **Next meeting: 2024/September/3rd(Tue) 0900-1000 CEST** + +* **Planned Meetings:** + * #23 September 17th + * #24 October 1st + * #25 October 15th + +* **EasyCLA** Please be informed that CAMARA easyCLA activation has been postponed to End of August. Please visit [EasyCLA test repo](https://github.com/camaraproject/EasyCLA) and test / initiate your CLA status. + + +## Action Items + +* **AI#21.01**: It was agreed to try to create test files by the deadline. Issues will be opened first. Fernando TEF for KYC Match, Toshi KDDI for KYC Fill-in. [Fernando TEF, Toshi KDDI] + +* **AI#21.02**: Fernando TEF will open a PR for Issue #134 (CountryMatchScore makes no sense), to incorporate this into Meta release. [Fernando TEF] + +* **AI#21.03**: Fernando TEF will open a PR for Issue #135 (Which fields are meant to be used for identification of the mobile phone user?), to incorporate this into Meta release. [Fernando TEF] + + +* **All remaining AIs** + +[END] diff --git a/original/KnowYourCustomer/documentation/MeetingMinutes/README.MD b/original/KnowYourCustomer/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomer/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomerAgeVerification/README.md b/original/KnowYourCustomerAgeVerification/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9a1936b3cbf72ea10c6b2db37d80d6baca975fa3 --- /dev/null +++ b/original/KnowYourCustomerAgeVerification/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# KnowYourCustomerAgeVerification + +Sandbox API Repository to describe, develop, document, and test the KnowYourCustomerAgeVerification Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/mYAzC) + +## Scope + +* Service API(s) “KnowYourCustomerAgeVerification” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases/tag/r1.3) (Fall25), with the following API versions: + * **kyc-age-verification v0.2.1** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerAgeVerification/blob/r1.3/code/API_definitions/kyc-age-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerAgeVerification/r1.3/code/API_definitions/kyc-age-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerAgeVerification/r1.3/code/API_definitions/kyc-age-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerAgeVerification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerAgeVerification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +* **Releases of the CAMARA KYC Age Verification API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification.yaml b/original/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification.yaml new file mode 100644 index 0000000000000000000000000000000000000000..48afcf1f289d70b881f21976e59c1ecefbde4db8 --- /dev/null +++ b/original/KnowYourCustomerAgeVerification/code/API_definitions/kyc-age-verification.yaml @@ -0,0 +1,513 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Age Verification + + description: | + + # Summary + This API provides the customer with the ability to check if the user of the line is older than a provided age, in order to provide API customer's age-restricted services, access to its age-restricted website etc.. + + # API functionality + + The API defines one service endpoint: + + - `POST /verify` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and checks if the age of the subscriber is older than the age threshold in the request. + Additionally, as optional function, provides (1) if age check is done against another form of official identification (Note) or not (verifiedStatus), (2) an overall score of how certain is the response using both information provided in the request and information that the Operator holds(identityMatchScore), (3) an indicator on whether the subscription has any kind of content lock (contentLock) and (4) an indicator on whether the subscription has any kind of parental control activated (parentalControl). + Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). [Required only in case a 2-legged flow has been agreed between API Provider and API Consumer following CAMARA directives; otherwise, phoneNumber must not be included] + - `ageThreshold`: The age threshold from which the age of the user must be compared. [Required] + - any of `idDocument`, `name`, `givenName`, `familyName`, `middleNames`, `familyNameAtBirth`, `birthdate`, `email`; additional subscriber's information to be checked in order to confirm that the subscriber is the contract's owner [Optional] + - `includeContentLock` and `includeParentalControl`: These two flags allow the API Client to indicate that the corresponding response properties `contentLock` and `parentalControl` should be returned. Its implementation is optional for the API Provider, so in such cases, these parameters will be ignored. [Optional] + + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `ageCheck`: Indicate 'true' when the age of the user is the same age or older than the age threshold (age >= age threshold), and 'false' if not (age < age threshold). Otherwise, 'not_available'. + - `verifiedStatus`: true if the information provided was checked against another form of official identification (Note), otherwise false. Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + - `identityMatchScore`: The overall score of identity information available in the Operator, information either provided in the request body comparing it to the one that the MNO holds or directly using internal MNO's information. It is optional for the Operator to return the Identity match score. + - `contentLock`: Indicates if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked). + - `parentalControl`: Indicates if the subscription associated with the phone number has any kind of parental control activated. + + ## Errors + + - If the authentication access token is not valid, a `401 UNAUTHENTICATED` error is returned + - If the API call contains a formatting or other any other syntactic error, a `400 INVALID_ARGUMENT` error is returned. + - If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + - If the API consumer has a valid access token that does not have the required scope to obtain Age Verification information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/KnowYourCustomerAgeVerification + +servers: + - url: "{apiRoot}/kyc-age-verification/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root + +tags: + - name: Age Verification + description: Operations to verify the age of a user. + +paths: + /verify: + post: + tags: + - Age Verification + summary: Verify Age Threshold + description: | + Verify that the age of the subscriber associated with a phone number is equal to or greater than the specified age threshold value. + + As it is possible that the person holding the contract and the end-user of the subscription may not be the same, the endpoint also admits a list of optional properties to be included in the request to improve the identification. The response may optionally include the `identityMatchScore` property with a value that indicates how certain it is that the information returned relates to the person that the API Client is requesting. To increase the reliability of the information returned, the API Provider may include in the response the `verifiedStatus` property, indicating whether the identity information in its possession has been verified against an identification document legally accepted as an age verification document (Note). Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + If the API Client indicates request properties `includeContentLock` or `includeParentalControl` with value `true` and the API Provider implements this functionality, then the response will also include `contentLock` and `parentalControl` properties to indicate if the subscription has any kind of content filtering enabled. On the other hand, if the request properties are not included or the API Client specifies value `false`, then the response properties will not be returned. If the API Provider doesn't implement this functionality, request properties will be ignored and response properties won't be returned in any case. + operationId: verifyAge + security: + - openId: + - kyc-age-verification:verify + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyRequestBody' + examples: + Two-Legged Access Token Example: + value: + ageThreshold: 18 + phoneNumber: '+34629255833' # Note: Only required in case a 2-legged flow has been agreed between API Provider and API Consumer; otherwise, do not include phoneNumber + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@example.com" + includeContentLock: true + includeParentalControl: true + Three-Legged Access Token Example: + value: + ageThreshold: 18 + idDocument: 66666666q + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + middleNames: Sanchez + familyNameAtBirth: YYYY + birthdate: '1978-08-22' + email: "federicaSanchez.Arjona@gmail.com" + includeContentLock: true + includeParentalControl: true + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyResponseBody' + examples: + KYC_200Example: + value: + ageCheck: "true" + verifiedStatus: true + identityMatchScore: 90 + contentLock: "false" + parentalControl: "true" + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + VerifyRequestBody: + type: "object" + description: Request to verify the age threshold provided. + required: + - ageThreshold + properties: + ageThreshold: + $ref: "#/components/schemas/AgeThreshold" + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + idDocument: + $ref: "#/components/schemas/IdDocument" + name: + $ref: "#/components/schemas/Name" + givenName: + $ref: "#/components/schemas/GivenName" + familyName: + $ref: "#/components/schemas/FamilyName" + middleNames: + $ref: "#/components/schemas/MiddleNames" + familyNameAtBirth: + $ref: "#/components/schemas/FamilyNameAtBirth" + birthdate: + $ref: "#/components/schemas/Birthdate" + email: + $ref: "#/components/schemas/Email" + includeContentLock: + $ref: "#/components/schemas/IncludeContentLock" + includeParentalControl: + $ref: "#/components/schemas/IncludeParentalControl" + + AgeThreshold: + type: "integer" + minimum: 0 + maximum: 120 + description: The age to be verified. The indicated range is a global definition of maximum and minimum values allowed to be requested. It is important to note that this range might be more restrictive in some implementations due to local regulations of a country i.e. A country does not allow to request for an age under 18. This limitation must be informed during the onboarding process. + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + IdDocument: + type: "string" + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + Name: + type: "string" + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + GivenName: + type: "string" + description: First/given name or compound first/given name of the customer. + + FamilyName: + type: "string" + description: Last name, family name, or surname of the customer. + + MiddleNames: + type: "string" + description: Middle name/s of the customer. + + FamilyNameAtBirth: + type: "string" + description: Last/family/sur- name at birth of the customer. + + Birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + Email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + IncludeContentLock: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `contentLock` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + IncludeParentalControl: + type: boolean + default: false + description: If this parameter is included in the request with value `true`, the response property `parentalControl` will be returned. If it is not included or its value is `false`, the response property will not be returned. + + VerifyResponseBody: + type: "object" + description: Response to an age verification request + required: + - ageCheck + properties: + ageCheck: + $ref: "#/components/schemas/AgeCheck" + verifiedStatus: + $ref: "#/components/schemas/VerifiedStatus" + identityMatchScore: + $ref: "#/components/schemas/IdentityMatchScore" + contentLock: + $ref: "#/components/schemas/ContentLock" + parentalControl: + $ref: "#/components/schemas/ParentalControl" + + AgeCheck: + type: "string" + description: Indicate `"true"` when the age of the user is the same age or older than the age threshold (age >= age threshold), and `"false"` if not (age < age threshold). If the API Provider doesn't have enough information to perform the validation, a `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + VerifiedStatus: + type: "boolean" + description: | + Indicate `true` if the information provided has been compared against information based on an identification document legally accepted as an age verification document (Note), otherwise indicate `false`. Note: Depending on the country, credit-check or other mechanism can be used instead of official identification for Age Verification. For details, please contact API Provider. + + IdentityMatchScore: + type: "integer" + minimum: 0 + maximum: 100 + description: The overall score of identity information available in the API Provider, information either provided in the request body comparing it to the one that the API Provider holds or directly using internal API Provider's information. It is optional for the API Provider to return the Identity match score. + + ContentLock: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of content lock (i.e certain web content blocked) and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ParentalControl: + type: "string" + description: Indicate `"true"` if the subscription associated with the phone number has any kind of parental control activated and `"false"` if not. If the information is not available the value `not_available` can be returned. + enum: + - 'true' + - 'false' + - 'not_available' + + ErrorInfo: + type: "object" + required: + - status + - code + - message + properties: + status: + type: "integer" + description: HTTP response status code + code: + type: "string" + description: A human-readable code to describe the error + message: + type: "string" + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token diff --git a/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md b/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..7a9ceedefa371a336637e0bce0a0df2c0eeaf20f --- /dev/null +++ b/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-age-verification v0.2.1 in release r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                public | stable
                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-age-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-age-verification.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/kyc-age-verification_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-age-verification.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/z4AzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story.md b/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..ea08c7bc98531e805e2799bc89d5107dc1738938 --- /dev/null +++ b/original/KnowYourCustomerAgeVerification/documentation/API_documentation/kyc-age-verification_User_Story.md @@ -0,0 +1,10 @@ +# KYC Age Verification API User Story + +| **Item** | **Details** | +|------|---------| +|_**Summary**_ | As an application developer of an age-restricted site or application, I want to verifiy the age of an End-User with Subcriber's information held by the MNO.| +|_**Roles, Actors and Scope**_ | **Roles:** End-User
                                                **Actors:** API Provider, API Consumer
                                                **Scope:** Any mobile phone line (not limited to 4G, 5G)| +|_**Pre-condition**_ | The preconditions are listed below:
                                                1. The End-User has provided mandatory/optional information of its identity to API Consumer
                                                2. API Consumer has onboarded to API Provider's API
                                                3. API Consumer has API credentials
                                                4. Privacy legal base requirement has been agreed between parties (End-User privacy)
                                                5. | +|_**Activities/Steps**_ | **Starts when:** The API Consumer application server makes a request to the Age Verification service (API) with the age restricted value.
                                                  **Ends when:** The API Provider service returns **_True_** if the age has been correctly verified else it returns **_False_**. Optionally the API Providers returns also an identityMatchScore, whether the data used has been verified, and whether a contentLock and parentalControl are in place. | +|_**Post-conditions**_ | The API Consumer can make decision to use the returned answer to follow-up its process. | +|_**Exceptions**_ | Several exceptions might occur during the KYC Age Verification API operations:
                                                  • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                  • Not Found: The phone number provided is not managed by the API Provider.
                                                  • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                  • | diff --git a/original/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README.MD b/original/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomerAgeVerification/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomerFill-in/README.md b/original/KnowYourCustomerFill-in/README.md new file mode 100644 index 0000000000000000000000000000000000000000..3ab5a3b24f9dd2ed10f4f648a772eb873526b29f --- /dev/null +++ b/original/KnowYourCustomerFill-in/README.md @@ -0,0 +1,56 @@ + + + + + + + + + +# KnowYourCustomerFill-in + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomerFill-in Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYAzC) + +## Scope + +* Service API(s) “KnowYourCustomerFill-in” (see APIBacklog.md) +* The API provides the API consumer with the ability to: + * request and receive the information for a particular end user, which is on file (and verified) by the end user's Operator in their own KYC records, in order for the service provider (API consumer) to confirm the accuracy of the information and provide a specific service to the end user. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/KnowYourCustomerFill-in/releases/tag/r1.3) (Fall25), with the following API versions: + * **kyc-fill-in v0.4.1** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerFill-in/blob/r1.3/code/API_definitions/kyc-fill-in.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerFill-in/r1.3/code/API_definitions/kyc-fill-in.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerFill-in/r1.3/code/API_definitions/kyc-fill-in.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerFill-in/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerFill-in/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerFill-in/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + +* Note: **Releases of the KnowYourCustomerFill-in API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) + +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/KnowYourCustomerFill-in/code/API_definitions/README.MD b/original/KnowYourCustomerFill-in/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/KnowYourCustomerFill-in/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in.yaml b/original/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in.yaml new file mode 100644 index 0000000000000000000000000000000000000000..89f110085f49d72580215ca77343243c01488891 --- /dev/null +++ b/original/KnowYourCustomerFill-in/code/API_definitions/kyc-fill-in.yaml @@ -0,0 +1,540 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Fill-in + + description: | + + This API provides the customer with the ability request and receive the information for a particular user, which on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + ## API Functionality + + This API allows API clients to request for API provider / MNO to provide information related to a mobile phone user, derived from the account data bound to their phone number. The API is intended to be used in the following scenario, for example: + + * To fill-in the user personal data during the digital registration of an account to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Fill-in_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contract with API provider/ Operator for use of this API. As that will depend on each API provider / MNO's business processes as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are to be defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. **As an important note**, capturing end user consent is necessary, because this API provides end user information (PII). + + * The above mentioned AuthN/AuthZ/End User consent capturing processes can give the API provider/ MNO the 3rd party identity (with the Access Token) and the end user identity (with the ID Token), so the API provider/ MNO can identify the 3rd party / enterprise customer and the end user. Then, it is up to API provider/ MNO to decide which information the 3rd party will receive by calling the API, and also the API provider / MNO is responsible for security and privacy issues. + + * For example, below is a potential operation: + * when making contract with API provider/ MNO, a 3rd party / enterprise customer receives its 3rd party identity and also decide which information (attributes) it will receive for its API call + * then, API provider / MNO will provide information (attributes) which the 3rd party / enterprise customer is allowed to receive by the contract. + + ### Special Scopes + + This API uses the following special scope `kyc-fill-in:set-all` which means that the API provider returns an API response as if all these scopes were specified in the scope value in the request: + + `kyc-fill-in:phoneNumber kyc-fill-in:idDocument kyc-fill-in:idDocumentType kyc-fill-in:idDocumentExpiryDate kyc-fill-in:name kyc-fill-in:givenName kyc-fill-in:familyName kyc-fill-in:nameKanaHankaku kyc-fill-in:nameKanaZenkaku kyc-fill-in:middleNames kyc-fill-in:familyNameAtBirth kyc-fill-in:address kyc-fill-in:streetName kyc-fill-in:streetNumber kyc-fill-in:postalCode kyc-fill-in:region kyc-fill-in:locality kyc-fill-in:country kyc-fill-in:houseNumberExtension kyc-fill-in:birthdate kyc-fill-in:email kyc-fill-in:gender kyc-fill-in:cityOfBirth kyc-fill-in:countryOfBirth kyc-fill-in:nationality` + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to request information related to an end user against the account data bound to their phone number. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/KnowYourCustomerFill-in + +servers: + - url: '{apiRoot}/kyc-fill-in/vwip' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Fill-in + description: Operations to provide information related to a customer identity stored the account data bound to the customer's phone number. + +paths: + /fill-in: + post: + tags: + - Fill-in + summary: Providing information related to a customer identity stored the account data bound to the customer's phone number. + + operationId: KYC_Fill-in + + security: + - openId: + - kyc-fill-in:set-all + - openId: + - kyc-fill-in:phoneNumber + - openId: + - kyc-fill-in:idDocument + - openId: + - kyc-fill-in:idDocumentType + - openId: + - kyc-fill-in:idDocumentExpiryDate + - openId: + - kyc-fill-in:name + - openId: + - kyc-fill-in:givenName + - openId: + - kyc-fill-in:familyName + - openId: + - kyc-fill-in:nameKanaHankaku + - openId: + - kyc-fill-in:nameKanaZenkaku + - openId: + - kyc-fill-in:middleNames + - openId: + - kyc-fill-in:familyNameAtBirth + - openId: + - kyc-fill-in:address + - openId: + - kyc-fill-in:streetName + - openId: + - kyc-fill-in:streetNumber + - openId: + - kyc-fill-in:postalCode + - openId: + - kyc-fill-in:region + - openId: + - kyc-fill-in:locality + - openId: + - kyc-fill-in:country + - openId: + - kyc-fill-in:houseNumberExtension + - openId: + - kyc-fill-in:birthdate + - openId: + - kyc-fill-in:email + - openId: + - kyc-fill-in:gender + - openId: + - kyc-fill-in:cityOfBirth + - openId: + - kyc-fill-in:countryOfBirth + - openId: + - kyc-fill-in:nationality + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_FillinRequest' + examples: + KYC_FillInBodyExample: + value: + {"phoneNumber": "+34629255833"} + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + + content: + application/json: + schema: + $ref: '#/components/schemas/KYC_FillinResponse' + examples: + KYC_Fillin200Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: '36' + birthdate: '1978-08-22' + email: abc@example.com + gender: MALE + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + KYC_FillinRequest: + type: object + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + KYC_FillinResponse: + type: object + properties: + + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the id_document of the customer stored on the Operator's system. + + idDocumentType: + type: string + enum: [passport, national_id_card, residence_permit, diplomatic_id, driver_licence, social_security_id, other] + description: Type of the official identity document provided. + + idDocumentExpiryDate: + type: string + format: date + description: Expiration date of the identity document (ISO 8601). + + name: + type: string + description: Complete name of the customer stored on the Operator's system. It is usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer on the Operator's system. + + familyName: + type: string + description: Last name, family name, or surname of the customer stored on the Operator's system. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan, stored on the Operator's system. + + middleNames: + type: string + description: Middle name/s of the customer stored on the Operator's system. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer stored on the Operator's system. + + address: + type: string + description: Complete address of the customer stored on the Operator's system. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address on the Operator's system. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address on the Operator's system. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: The postal code or Zip code of the customer's address, stored on the Operator's system. + + region: + type: string + description: Region/prefecture of the customer's address, stored on the Operator's system. + + locality: + type: string + description: Locality of the customer's address, stored on the Operator's system. + + country: + type: string + description: Country of the customer's address stored on the Operator's system. Format ISO 3166-1 alpha-2. + + houseNumberExtension: + type: string + description: House number extension of the customer stored on the Operator's system. Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: Birthdate of the customer, in ISO 8601 calendar date format (YYYY-MM-DD), stored on the Operator's system. + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain), stored on the Operator's system. + + gender: + type: string + description: Gender of the customer stored on the Operator's system (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + cityOfBirth: + type: string + description: City where the customer was born. + + countryOfBirth: + type: string + description: Country where the customer was born. Format ISO 3166-1 alpha-2. + + nationality: + type: string + description: ISO 3166-1 alpha-2 code of the customer’s nationality. In the case a customer has more than one nationality, it is supposed to be the nationality related to the ID document provided in the match request. + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token diff --git a/original/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story.md b/original/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..158abcbb16059c1c98cf16dbadb13873ee5afc02 --- /dev/null +++ b/original/KnowYourCustomerFill-in/documentation/API_documentation/KnowYourCustomer_User_Story.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
                                                    + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                    **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                    **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The Customer:User has provided mandatory information of their identity
                                                    2. Application developer has onboarded to MNO API
                                                    3. Application developer has API credentials
                                                    4. Privacy legal base requirement has been solved (Customer privacy)
                                                    | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
                                                    **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
                                                    | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
                                                    • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                    • Not Found: The number provided is not managed by the MNO
                                                    • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                    | + +

                                                    + +**User Story: KYC Fill-In - Get identity information of customer** +
                                                    + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                    **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                    **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The Customer:User has provided mandatory information of their identity
                                                    2. Application developer has onboarded to MNO API
                                                    3. Application developer has API credentials
                                                    4. Privacy legal base requirement has been solved (Customer privacy)
                                                    | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
                                                    **Ends when:** The MNO service returns the identity information stored in its customer database.
                                                    | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
                                                    • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                    • Not Found: The number provided is not managed by the MNO
                                                    • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                    | + + diff --git a/original/KnowYourCustomerFill-in/documentation/API_documentation/README.MD b/original/KnowYourCustomerFill-in/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomerFill-in/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md b/original/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ad22989d14bad14148960094bd8b7aa0f6404c4a --- /dev/null +++ b/original/KnowYourCustomerFill-in/documentation/API_documentation/kyc-fill-in-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-fill-in 0.4.1 in release r1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-fill-in.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-fill-in.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-fill-in.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/d4AzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/KnowYourCustomerFill-in/documentation/SupportingDocuments/README.MD b/original/KnowYourCustomerFill-in/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomerFill-in/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomerMatch/README.md b/original/KnowYourCustomerMatch/README.md new file mode 100644 index 0000000000000000000000000000000000000000..64b0bf3f25c6ab19bad940077a2638ec7835e1a8 --- /dev/null +++ b/original/KnowYourCustomerMatch/README.md @@ -0,0 +1,55 @@ + + + + + + + + + +# KnowYourCustomerMatch + +Incubating API Repository to evolve and maintain the definitions and documentation of KnowYourCustomerMatch Service API(s) within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/80117795/Know+Your+Customer) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/EQAzC) + +## Scope + +* Service API(s) “KnowYourCustomerMatch” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * compare the information that the Service Provider (SP) has for a particular user with that on file (and verified) by the user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the user. +* Describe, develop, document, and test the API(s) +* Started: September 2023 (within [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer)) +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/KnowYourCustomerMatch/releases/tag/r1.2) (Fall25), with the following API versions: + * **kyc-match v0.4.0** + [[YAML]](https://github.com/camaraproject/KnowYourCustomerMatch/blob/r1.2/code/API_definitions/kyc-match.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerMatch/r1.2/code/API_definitions/kyc-match.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/KnowYourCustomerMatch/r1.2/code/API_definitions/kyc-match.yaml) +* The latest public release is always available here: https://github.com/camaraproject/KnowYourCustomerMatch/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/KnowYourCustomerMatch/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/KnowYourCustomerMatch/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + +* Note: **Releases of the KnowYourCustomerMatch API until Spring25 are available in [KnowYourCustomer](https://github.com/camaraproject/KnowYourCustomer).** + +## Contributing + +* Meetings are held virtually + + * Schedule: bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST). For date/time of the next meeting, see previous meeting minutes. + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Access [Meeting Minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14551060/KnowYourCustomer+Meeting+Minutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/KnowYourCustomerMatch/code/API_definitions/README.MD b/original/KnowYourCustomerMatch/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/KnowYourCustomerMatch/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/KnowYourCustomerMatch/code/API_definitions/kyc-match.yaml b/original/KnowYourCustomerMatch/code/API_definitions/kyc-match.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fad948747a03a6f7cb98d152c7d1c03dc44cb500 --- /dev/null +++ b/original/KnowYourCustomerMatch/code/API_definitions/kyc-match.yaml @@ -0,0 +1,696 @@ +openapi: 3.0.3 +info: + title: Know Your Customer Match + + description: | + + This API provides the customer with the ability to compare the information it (Service Provider, SP) has for a particular mobile phone user with that on file (and verified) by the mobile phone user's Operator in their own KYC records, in order for the SP to confirm the accuracy of the information and provide a specific service to the mobile phone user. + + ## Relevant Definitions and concepts + + * **KYC**: stands for Know Your Customer and it is the process of a business verifying the identity of their clients and assessing their suitability, along with the potential risks of illegal intentions towards the business relationship. + + * **Match Score**: a numerical value that quantifies the similarity between two pieces of text based on the words they contain. This score is often used in various applications like text comparison, plagiarism detection, information retrieval, and natural language processing. The score typically reflects how well the words in one text match the words in another text. In the context of this API, this score will be used to determine how much does the input information looks like the information stored in the Operator's system. Unless otherwise captured in the implementation notes which Operators may publish, score will use the Jaro-Winkler distance algorithm for all countries. This parameter, as optional, will be returned depending on the capability of the Operator to calculate the scoring value. This means that not all Operators will implement this functionality or won't have the requested parameter available. It can happen that an Operator implements the score functionality but, for whatever reason, is not able to calculate it based on the client's input or the related stored information. For these cases, the score property related won't be returned in the response. + The range of score values is between "0" and "100", where higher scores indicate a higher similarity between the two compared parameters. + + ## API Functionality + + This API allows API clients to verify the matching of a number of attributes related to a customer identity against the account data bound to their phone number. The API is intended to be used in the following scenarios, for example: + + * To verify the user personal data during the digital registration of an account to a 3rd party service. + + * To prevent fraud, wrong or imprecise information, and/or facilitate the onboarding of a mobile phone user to a 3rd party service. + + The following figure is the generic high-level flows of this API. + + KYC_Match_flow + + Note: + + * Before calling this API, 3rd parties / enterprise customers who want to use this API should make contact with API provider/ MNO for use of this API. As that will depend on each API provider / MNO's business process as well as GSMA Open Gateway standard process, it is out of scope of this API definition. + + * When calling this API, at the beginning, there should be required processes for Authentication / Authorisation / End User Consent capturing. As those processes are defined as CAMARA commonality standards, they are out of scope of this API definition, however, use of the OpenID Connect (OIDC) is stated as security scheme. + + ## Resources and Operations overview + + The API provides the following endpoint: + + * An endpoint to verify the matching of a number of attributes related to a mobile phone user identity against the account data bound to their phone number. + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + version: wip + x-camara-commonalities: 0.6 + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/KnowYourCustomerMatch + +servers: + - url: '{apiRoot}/kyc-match/v0.4' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Match + description: Operations to match a customer identity against the account data bound to their phone number. + +paths: + /match: + post: + tags: + - Match + summary: Matching a customer identity by checking a set of attributes related against the account data bound to their phone number. + description: |- + Verify matching of a number of attributes related to a customer identity against the verified data bound to their phone number in the Operator systems. Regardless of whether the `phoneNumber` is explicitly stated in the request body, at least one of the other fields must be provided, otherwise a `HTTP 400 - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION` error will be returned. + + The API will return the result of the matching process for each requested attribute. This means that the response will **only** contain the attributes for which validation has been requested. Possible values are: + - **true**: the attribute provided matches with the one in the Operator systems, which is equal to a `match_score` of 100. + - **false**: the attribute provided does not match with the one in the Operator systems. + - **not_available**: the attribute is not available to validate. + operationId: KYC_Match + + security: + - openId: + - kyc-match:match + + + parameters: + - $ref: '#/components/parameters/x-correlator' + + requestBody: + required: true + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchRequestBody' + examples: + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: '+34629255833' + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + Three-Legged Without Phone Number Example: + value: + idDocument: 66666666q + idDocumentType: passport + idDocumentExpiryDate: '2027-07-12' + name: Federica Sanchez Arjona + givenName: Federica + familyName: Sanchez Arjona + nameKanaHankaku: federica + nameKanaZenkaku: Federica + middleNames: Sanchez + familyNameAtBirth: YYYY + address: Tokyo-to Chiyoda-ku Iidabashi 3-10-10 + streetName: Nicolas Salmeron + streetNumber: '4' + postalCode: '1028460' + region: Tokyo + locality: ZZZZ + country: JP + houseNumberExtension: VVVV + birthdate: '1978-08-22' + email: abc@example.com + gender: OTHER + cityOfBirth: Madrid + countryOfBirth: ES + nationality: ES + + responses: + '200': + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + + content: + application/json: + + schema: + $ref: '#/components/schemas/KYC_MatchResponse' + examples: + KYC_Match200Example: + value: + idDocumentMatch: 'true' + idDocumentTypeMatch: 'true' + idDocumentExpiryDateMatch: 'true' + nameMatch: 'true' + givenNameMatch: 'not_available' + familyNameMatch: 'not_available' + nameKanaHankakuMatch: 'true' + nameKanaZenkakuMatch: 'false' + middleNamesMatch: 'true' + familyNameAtBirthMatch: 'false' + familyNameAtBirthMatchScore: 90 + addressMatch: 'true' + streetNameMatch: 'true' + streetNumberMatch: 'true' + postalCodeMatch: 'true' + regionMatch: 'true' + localityMatch: 'not_available' + countryMatch: 'true' + houseNumberExtensionMatch: 'not_available' + birthdateMatch: 'false' + emailMatch: 'false' + emailMatchScore: 87 + genderMatch: 'false' + cityOfBirthMatch: 'false' + cityOfBirthMatchScore: 86 + countryOfBirthMatch: 'true' + nationalityMatch: 'true' + + '400': + $ref: '#/components/responses/Generic400' + + '401': + $ref: '#/components/responses/Generic401' + + '403': + $ref: '#/components/responses/Generic403' + + '404': + $ref: '#/components/responses/Generic404' + + '422': + $ref: '#/components/responses/Generic422' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + KYC_MatchRequestBody: + type: object + description: Payload to validate the customer data. + + properties: + phoneNumber: + type: string + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + idDocument: + type: string + description: Id number associated to the official identity document in the country. It may contain alphanumeric characters. + + idDocumentType: + type: string + enum: [passport, national_id_card, residence_permit, diplomatic_id, driver_licence, social_security_id, other] + description: Type of the official identity document provided. + + idDocumentExpiryDate: + type: string + format: date + description: Expiration date of the identity document (ISO 8601). + + name: + type: string + description: Complete name of the customer, usually composed of first/given name and last/family/sur- name in a country. Depending on the country, the order of first/give name and last/family/sur- name varies, and middle name could be included. It can use givenName, middleNames, familyName and/or familyNameAtBirth. For example, in ESP, name+familyName; in NLD, it can be name+middleNames+familyName or name+middleNames+familyNameAtBirth, etc. + + givenName: + type: string + description: First/given name or compound first/given name of the customer. + + familyName: + type: string + description: Last name, family name, or surname of the customer. + + nameKanaHankaku: + type: string + description: Complete name of the customer in Hankaku-Kana format (reading of name) for Japan. + + nameKanaZenkaku: + type: string + description: Complete name of the customer in Zenkaku-Kana format (reading of name) for Japan. + + middleNames: + type: string + description: Middle name/s of the customer. + + familyNameAtBirth: + type: string + description: Last/family/sur- name at birth of the customer. + + address: + type: string + description: Complete address of the customer. For some countries, it is built following the usual concatenation of parameters in a country, but for other countries, this is not the case. For some countries, it can use streetName, streetNumber and/or houseNumberExtension. For example, in ESP, streetName+streetNumber; in NLD, it can be streetName+streetNumber or streetName+streetNumber+houseNumberExtension. + + streetName: + type: string + description: Name of the street of the customer's address. It should not include the type of the street. + + streetNumber: + type: string + description: The street number of the customer's address. Number identifying a specific property on the 'streetName'. + + postalCode: + type: string + description: Zip code or postal code + + region: + type: string + description: Region/prefecture of the customer's address + + locality: + type: string + description: Locality of the customer's address + + country: + type: string + description: Country of the customer's address. Format ISO 3166-1 alpha-2 + + houseNumberExtension: + type: string + description: Specific identifier of the house needed depending on the property type. For example, number of apartment in an apartment building. + + birthdate: + type: string + format: date + description: The birthdate of the customer, in RFC 3339 / ISO 8601 calendar date format (YYYY-MM-DD). + + email: + type: string + format: email + description: Email address of the customer in the RFC specified format (local-part@domain). + + gender: + type: string + description: Gender of the customer (Male/Female/Other). + enum: + - MALE + - FEMALE + - OTHER + + cityOfBirth: + type: string + description: City where the customer was born. + + countryOfBirth: + type: string + description: Country where the customer was born. Format ISO 3166-1 alpha-2. + + nationality: + type: string + description: ISO 3166-1 alpha-2 code of the customer’s nationality. In the case a customer has more than one nationality, it is supposed to be the nationality related to the ID document provided in the match request. + MatchResult: + type: string + description: | + true - the attribute provided matches with the one in the Operator systems, which is equal to a `match_score` of 100. + false - the attribute provided does not match with the one in the Operator systems. + not_available - the attribute is not available to validate. + enum: + - 'true' + - 'false' + - 'not_available' + + MatchScoreResult: + type: integer + description: | + Indicates the similarity score assigned to the input value when it does not exactly match the value stored in the operator's system. + This property shall only be returned when the value of the corresponding match field is `false`. + A perfect match with a score of 100 is indicated by `match` being 'true' and no `matchScore` is returned in this case. + minimum: 0 + maximum: 99 + + KYC_MatchResponse: + type: object + properties: + idDocumentMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether Id number associated to the ID document of the customer matches with the one on the Operator's system. + idDocumentTypeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether document type associated to the ID document of the customer matches with the one on the Operator's system. + idDocumentExpiryDateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether document expiration date associated to the ID document of the customer matches with the one on the Operator's system. + nameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the complete name of the customer matches with the one on the Operator's system. + nameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + givenNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether First name/given name of the customer matches with the one on the Operator's system. + givenNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether last name/ family name/ surname of the customer matches with the one on the Operator's system. + familyNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaHankakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Hankaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaHankakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + nameKanaZenkakuMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete name of the customer in Zenkaku-Kana format (reading of name) for Japan matches with the one on the Operator's system. + nameKanaZenkakuMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + middleNamesMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the middle names of the customer matches with the one on the Operator's system. + middleNamesMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + familyNameAtBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the Family Name At Birth of the customer matches with the one on the Operator's system. + familyNameAtBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + addressMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether complete address of the customer matches with the one on the Operator's system. + addressMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNameMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street name of the customer matches with the one on the Operator's system. + streetNameMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + streetNumberMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the street number of the customer matches with the one on the Operator's system. + streetNumberMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + postalCodeMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the postal code / zip code of the customer matches with the one on the Operator's system. + regionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the region of the customer's address matches with the one on the Operator's system. + regionMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + localityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the locality of the customer's address matches with the one on the Operator's system. + localityMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country of the customer's address matches with the one on the Operator's system. + houseNumberExtensionMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the house number extension of the customer's address with the one on the Operator's system. + birthdateMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the birthdate of the customer matches with the one on the Operator's system. + emailMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the email address of the customer matches with the one on the Operator's system. + emailMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + genderMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the gender of the customer matches with the one on the Operator's system. + cityOfBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the city at birth of the customer matches with the one on the Operator's system + cityOfBirthMatchScore: + $ref: '#/components/schemas/MatchScoreResult' + countryOfBirthMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the country at birth of the customer matches with the one on the Operator's system + nationalityMatch: + allOf: + - $ref: '#/components/schemas/MatchResult' + - description: Indicates whether the nationality of the customer matches with the one on the Operator's system + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + message: + type: string + description: A human-readable description of what the event represents + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION: + description: Indicated param combination is invalid + value: + status: 400 + code: KNOW_YOUR_CUSTOMER.INVALID_PARAM_COMBINATION + message: Indicated parameter combination is invalid + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided diff --git a/original/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story.md b/original/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..158abcbb16059c1c98cf16dbadb13873ee5afc02 --- /dev/null +++ b/original/KnowYourCustomerMatch/documentation/API_documentation/KnowYourCustomer_User_Story.md @@ -0,0 +1,27 @@ +**User Story: KYC Match - verify customer information** +
                                                    + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to confirm (using my application server/backend service) the identity of a customer by comparison to MNO user's information. Information which could be provided are phone number, given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                    **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                    **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The Customer:User has provided mandatory information of their identity
                                                    2. Application developer has onboarded to MNO API
                                                    3. Application developer has API credentials
                                                    4. Privacy legal base requirement has been solved (Customer privacy)
                                                    | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the KYC service (API) to confirm user identity.
                                                    **Ends when:** The MNO service returns matching result for each attribute of the customer identity.
                                                    | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the KYC Match API operations:
                                                    • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                    • Not Found: The number provided is not managed by the MNO
                                                    • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                    | + +

                                                    + +**User Story: KYC Fill-In - Get identity information of customer** +
                                                    + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to retreive (using my application server/backend service) the identity information of a user by requesting the MNO to query information stored in its customer database. Information returned by the MNO are given name, family name, street address, city, country, region, postal code, birthdate, email address, etc. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                    **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                    **Scope:** Any phone line (not limlited to 4G, 5G) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The Customer:User has provided mandatory information of their identity
                                                    2. Application developer has onboarded to MNO API
                                                    3. Application developer has API credentials
                                                    4. Privacy legal base requirement has been solved (Customer privacy)
                                                    | +| ***Activities/Steps*** | **Starts when:** The third party/enterprise customer application server makes a request to the KYC service (API) to retreive user identity information.
                                                    **Ends when:** The MNO service returns the identity information stored in its customer database.
                                                    | +| ***Post-conditions*** | The application developer uses this customer data to follow-up the enterprise process | +| ***Exceptions*** | Several exceptions might occur during the KYC Fill-in API operations:
                                                    • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                    • Not Found: The number provided is not managed by the MNO
                                                    • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                    | + + diff --git a/original/KnowYourCustomerMatch/documentation/API_documentation/README.MD b/original/KnowYourCustomerMatch/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomerMatch/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md b/original/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..8f7f36503b2e67e87688ca112b38ba2636ccf041 --- /dev/null +++ b/original/KnowYourCustomerMatch/documentation/API_documentation/kyc-match-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for kyc-match 0.4.0 in release r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/kyc-match.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/kyc-match.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/KnowYourCustomer_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/kyc-match.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/RwAzC) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/KnowYourCustomerMatch/documentation/SupportingDocuments/README.MD b/original/KnowYourCustomerMatch/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/KnowYourCustomerMatch/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ModelAsAService/README.md b/original/ModelAsAService/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9f8603e9b809e693008ec43c83155ddd02028348 --- /dev/null +++ b/original/ModelAsAService/README.md @@ -0,0 +1,64 @@ + + + + + + + + + +# ModelAsAService + +Sandbox API Repository to describe, develop, document, and test the ModelAsAService Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/_4AjAw) + +## Scope + +* Service APIs “ModelAsAService” (see APIBacklog.md) +* MaaS (Model as a Services) refers to the packaging of AI models and their associated capabilities into reusable services, enabling users to quickly and efficiently build, deploy, monitor, and invoke models without the need to develop and maintain underlying foundational capabilities. +* The API provides the API consumer with the ability to: + * build and manage personalized Knowledge Bases (knowledge-base) + * quickly construct unique Q&A Assistant applications (qa-assistant-manage) + * provide Q&A services to the users of the application (qa-assistant-service) + * NOTE: more model services to be added. +* Describe, develop, document, and test the APIs +* Started: November 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/ModelAsAService/releases/tag/r1.2) (Fall25), with the following API versions: + * **knowledge-base v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/knowledge-base.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/knowledge-base.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/knowledge-base.yaml) + * **qa-assistant-manage v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/qa-assistant-manage.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-manage.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-manage.yaml) + * **qa-assistant-service v0.1.0** + [[YAML]](https://github.com/camaraproject/ModelAsAService/blob/r1.2/code/API_definitions/qa-assistant-service.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-service.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/ModelAsAService/r1.2/code/API_definitions/qa-assistant-service.yaml) +* The latest public release is always available here: https://github.com/camaraproject/ModelAsAService/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/ModelAsAService/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/ModelAsAService/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly (odd weeks), Tuesday, 09:00 UTC (11:00 UTC+2, 17:00 UTC+8) + * [Join](https://teams.live.com/meet/9374614741908?p=QFhUf7b0SHZRdXSfA6) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/GpKaVSqC) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/ModelAsAService/code/API_definitions/README.MD b/original/ModelAsAService/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/ModelAsAService/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/ModelAsAService/code/API_definitions/knowledge-base.yaml b/original/ModelAsAService/code/API_definitions/knowledge-base.yaml new file mode 100644 index 0000000000000000000000000000000000000000..c2735638f91e962889ca48182967f83c6a0ba5e2 --- /dev/null +++ b/original/ModelAsAService/code/API_definitions/knowledge-base.yaml @@ -0,0 +1,624 @@ +openapi: 3.0.3 +info: + title: Knowledge Base + description: >- + This API offers comprehensive CRUD (Create, Read, Update, Delete) management capabilities for the knowledge base, along with document uploading functionality. + It is designed to provide applications with standardized capabilities for knowledge content storage and management, supporting multi-format document storage, fine-grained permission control, and end-to-end traceability. + It is suitable for building knowledge-intensive systems (such as intelligent customer service platforms and enterprise document platforms) while ensuring compliance. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## API Functionality + + This API allows the API consumer to perform CRUD operations on the knowledge base hosted on the server. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scopes are required: + - knowledge-base:knowledge-bases:create - Create new knowledge bases + - knowledge-base:knowledge-bases:read - Read knowledge base entries + - knowledge-base:knowledge-bases:update - Update existing knowledge bases + - knowledge-base:knowledge-bases:delete - Delete knowledge bases + - knowledge-base:documents:update - Upload documents to knowledge bases + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/knowledge-base/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Knowledge Base + description: Knowledge base management + +paths: + /knowledge-bases: + post: + operationId: createKnowledgeBase + summary: Create a new knowledge base + description: | + Creates a new knowledge base with the provided metadata. + + **Key Features:** + - Initializes a new knowledge base container + - Stores name and description metadata + - Generates unique knowledgeBaseId + + **Key Rules:** + - Requires `name` field in request body + - Requires `knowledge-base:knowledge-bases:create` scope + - Name must be unique within the system + + **Response Characteristics:** + - **201 Created**: Returns full `KnowledgeBase` object with generated ID + - **400 Bad Request**: Missing `name` or invalid parameters + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Backend processing failure + tags: + - Knowledge Base + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:knowledge-bases:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBaseCreateRequest' + responses: + '201': + description: Knowledge base created successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + get: + operationId: listKnowledgeBases + summary: Get all knowledge bases + description: | + Retrieves all knowledge bases accessible to the authenticated user. + + **Key Features:** + - Returns complete collection of knowledge bases + - Includes metadata and document lists + - Supports pagination (implied by array response) + + **Key Rules:** + - Requires `knowledge-base:knowledge-bases:read` scope + - Returns empty array if no knowledge bases exist + + **Response Characteristics:** + - **200 OK**: Array of `KnowledgeBase` objects + - **401 Unauthenticated**: Invalid/missing credentials + - **403 Forbidden**: Insufficient permissions + - **500 Internal Server Error**: Data retrieval failure + tags: + - Knowledge Base + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:knowledge-bases:read + responses: + '200': + description: List of knowledge bases + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + /knowledge-bases/{knowledgeBaseId}: + parameters: + - name: knowledgeBaseId + in: path + required: true + schema: + type: string + description: ID of the knowledge base + - $ref: '#/components/parameters/x-correlator' # Added correlator + + get: + operationId: getKnowledgeBase + summary: Get a specific knowledge base + description: | + Retrieves metadata and document list for a specific knowledge base. + + **Key Features:** + - Returns detailed metadata (name, description) + - Includes list of documents with filenames/formats + - Provides document upload timestamps + + **Key Rules:** + - Requires valid `knowledgeBaseId` path parameter + - Requires `knowledge-base:knowledge-bases:read` scope + + **Response Characteristics:** + - **200 OK**: Complete `KnowledgeBase` object + - **404 Not Found**: Invalid/non-existent knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Data retrieval failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:read + responses: + '200': + description: Knowledge base details + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + put: + operationId: updateKnowledgeBase + summary: Update a knowledge base + description: | + Updates metadata of an existing knowledge base. + + **Key Features:** + - Modifies name and/or description + - Preserves existing document associations + - Returns updated metadata + + **Key Rules:** + - Requires at least one update field (name/description) + - Requires `knowledge-base:knowledge-bases:update` scope + - knowledgeBaseId must exist + + **Response Characteristics:** + - **200 OK**: Updated `KnowledgeBase` object + - **400 Bad Request**: No update fields provided + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Update processing failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:update + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBaseUpdateRequest' + responses: + '200': + description: Knowledge base updated successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/KnowledgeBase' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + delete: + operationId: deleteKnowledgeBase + summary: Delete a knowledge base + description: | + Permanently deletes a knowledge base and its documents. + + **Key Features:** + - Removes knowledge base metadata + - Deletes all associated documents + - Irreversible operation + + **Key Rules:** + - Requires valid `knowledgeBaseId` + - Requires `knowledge-base:knowledge-bases:delete` scope + - No partial deletions + + **Response Characteristics:** + - **204 No Content**: Successful deletion (no body) + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Deletion processing failure + tags: + - Knowledge Base + security: + - openId: + - knowledge-base:knowledge-bases:delete + responses: + '204': + description: Knowledge base deleted successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + /knowledge-bases/{knowledgeBaseId}/documents: + post: + operationId: uploadDocument + summary: Upload a document to a knowledge base + description: | + Uploads a document to a knowledge base. + + **Key Features:** + - Supports doc/pdf/txt/csv formats + - Stores filename and format metadata + - Records upload timestamp + + **Key Rules:** + - Requires valid `knowledgeBaseId` + - Requires `knowledge-base:documents:update` scope + - File must be sent as multipart/form-data + - Maximum file size determined by implementation + + **Response Characteristics:** + - **201 Created**: Success message with filename + - **400 Bad Request**: Invalid file format + - **415 Unsupported Media Type**: Unacceptable format + - **404 Not Found**: Invalid knowledgeBaseId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Storage failure + tags: + - Documents + parameters: + - name: knowledgeBaseId + in: path + required: true + schema: + type: string + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - knowledge-base:documents:update + requestBody: + content: + multipart/form-data: + schema: + type: object + properties: + document: + type: string + format: binary + required: + - document + required: true + responses: + '201': + description: Document uploaded successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: object + properties: + message: + type: string + example: "Document uploaded successfully" + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '415': + $ref: '#/components/responses/Generic415' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for request tracing + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + KnowledgeBase: + type: object + properties: + knowledgeBaseId: + type: string + description: Unique identifier of the knowledge base + name: + type: string + description: Name of the knowledge base + description: + type: string + description: Detailed description of the knowledge base + documents: + type: array + items: + type: object + properties: + filename: + type: string + format: + type: string + enum: [doc, pdf, txt, csv] + description: File format + uploadDate: + type: string + format: date-time + description: "Upload timestamp. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ" + description: List of documents in the knowledge base + + KnowledgeBaseCreateRequest: + type: object + required: + - name + properties: + name: + type: string + description: Name of the knowledge base + description: + type: string + description: Detailed description of the knowledge base + + KnowledgeBaseUpdateRequest: + type: object + properties: + name: + type: string + description: New name of the knowledge base + description: + type: string + description: New description of the knowledge base + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_DOCUMENT_FORMAT + - MISSING_REQUIRED_PARAM + examples: + GENERIC_400_INVALID_DOCUMENT_FORMAT: + description: Invalid document format + value: + status: 400 + code: INVALID_DOCUMENT_FORMAT + message: "Invalid document format. Supported formats: doc/pdf/txt/csv" + GENERIC_400_MISSING_REQUIRED_PARAM: + description: Missing required parameter + value: + status: 400 + code: MISSING_REQUIRED_PARAM + message: "Required parameter 'name' is missing" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions for this operation + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - KNOWLEDGE_BASE_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_KNOWLEDGE_BASE_NOT_FOUND: + description: Knowledge base not found + value: + status: 404 + code: KNOWLEDGE_BASE_NOT_FOUND + message: "Specified knowledge base ID does not exist" + + Generic415: + description: Unsupported media type + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 415 + code: + enum: + - UNSUPPORTED_MEDIA_TYPE + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Unsupported document format + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: "Unsupported document format. Supported formats: doc/pdf/txt/csv" + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred" diff --git a/original/ModelAsAService/code/API_definitions/qa-assistant-manage.yaml b/original/ModelAsAService/code/API_definitions/qa-assistant-manage.yaml new file mode 100644 index 0000000000000000000000000000000000000000..3172fd7de48feec7b8d184a543900e49acbfbec6 --- /dev/null +++ b/original/ModelAsAService/code/API_definitions/qa-assistant-manage.yaml @@ -0,0 +1,626 @@ +openapi: 3.0.3 +info: + title: Q&A Assistant - Manage + description: >- + This API provides CRUD (Create, Read, Update, Delete) management functions for the Question and Answer (Q&A) Assistant, aiming to equip developers with the capability to configure and manage intelligent question-answering systems based on Large Language Models (LLMs). + It supports model parameter tuning, knowledge base association, and prompt engineering configuration, making it suitable for building customizable intelligent customer service or question-answering services. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scopes are required: + - qa-assistant-manage:assistants:create - Create new assistants + - qa-assistant-manage:assistants:read - Read assistant details + - qa-assistant-manage:assistants:update - Update existing assistants + - qa-assistant-manage:assistants:delete - Delete assistants + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/qa-assistant-manage/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /assistants: + post: + operationId: createAssistant + summary: Create a new QA assistant + description: | + Creates a new QA assistant configuration. + + **Key Features:** + - Configures LLM parameters (model, temperature, max_tokens) + - Associates with knowledge bases + - Sets behavior-defining prompts + + **Key Rules:** + - Requires `name`, `configurationPrompt`, and `largeModelParameters` + - `largeModelParameters` must include `model`, `temperature` (0.0-1.0), `max_tokens` (≥1) + - Needs `qa-assistant-manage:assistants:create` scope + + **Response Characteristics:** + - **201 Created**: Returns `AssistantResponse` with generated assistantId + - **400 Bad Request**: Missing parameters or invalid values (e.g., temperature out of range) + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Assistant creation failure + tags: + - Assistants + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-manage:assistants:create + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantCreateRequest' + responses: + '201': + description: Assistant created successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + get: + operationId: listAssistants + summary: List all QA assistants + description: | + Retrieves all configured QA assistants. + + **Key Features:** + - Returns complete assistant configurations + - Includes metadata (createdAt, updatedAt) + - Shows associated knowledge bases + + **Key Rules:** + - Requires `qa-assistant-manage:assistants:read` scope + - Returns empty array if no assistants exist + + **Response Characteristics:** + - **200 OK**: Array of `Assistant` objects + - **401 Unauthenticated**: Invalid credentials + - **403 Forbidden**: Insufficient permissions + - **500 Internal Server Error**: Data retrieval failure + tags: + - Assistants + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-manage:assistants:read + responses: + '200': + description: List of assistants + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/Assistant' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '500': + $ref: '#/components/responses/Generic500' + + /assistants/{assistantId}: + parameters: + - name: assistantId + in: path + required: true + schema: + type: string + description: Unique identifier of the assistant + - $ref: '#/components/parameters/x-correlator' # Added correlator + + get: + operationId: getAssistant + summary: Get a specific QA assistant + description: | + Retrieves detailed configuration for a specific assistant. + + **Key Features:** + - Returns full LLM parameter configuration + - Includes knowledge base associations + - Shows prompt configurations + + **Key Rules:** + - Requires valid UUID `assistantId` + - Needs ` knowledge-base:documents:update` scope + + **Response Characteristics:** + - **200 OK**: Complete `Assistant` object + - **404 Not Found**: Invalid/non-existent assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Configuration retrieval failure + tags: + - Assistants + security: + - openId: + - knowledge-base:documents:update + responses: + '200': + description: Assistant details + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/Assistant' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + put: + operationId: updateAssistant + summary: Update a QA assistant + description: | + Modifies an existing QA assistant configuration. + + **Key Features:** + - Updates LLM parameters dynamically + - Changes knowledge base associations + - Modifies behavior prompts + + **Key Rules:** + - Requires valid UUID `assistantId` + - At least one update field must be provided + - Parameter values must meet constraints (e.g., temperature 0.0-1.0) + - Needs `qa-assistant-manage:assistants:update` scope + + **Response Characteristics:** + - **200 OK**: Returns updated `AssistantResponse` + - **400 Bad Request**: Invalid parameters or no update fields + - **404 Not Found**: Invalid assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Update processing failure + tags: + - Assistants + security: + - openId: + - qa-assistant-manage:assistants:update + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantUpdateRequest' + responses: + '200': + description: Assistant updated successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AssistantResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + + delete: + operationId: deleteAssistant + summary: Delete a QA assistant + description: | + Permanently removes a QA assistant configuration. + + **Key Features:** + - Irreversible deletion + - Cleans up associated resources + - Immediate deactivation + + **Key Rules:** + - Requires valid UUID `assistantId` + - Needs `qa-assistant-manage:assistants:delete` scope + - Cannot be undone + + **Response Characteristics:** + - **204 No Content**: Successful deletion (no body) + - **404 Not Found**: Invalid assistantId + - **403 Forbidden**: Missing required scope + - **500 Internal Server Error**: Deletion processing failure + tags: + - Assistants + security: + - openId: + - qa-assistant-manage:assistants:delete + responses: + '204': + description: Assistant deleted successfully + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + AssistantCreateRequest: + type: object + required: + - name + - configurationPrompt + - largeModelParameters + properties: + name: + type: string + description: Name of the assistant + description: + type: string + description: Description of the assistant + knowledgeBaseId: + type: string + description: Optional ID of the associated knowledge base + configurationPrompt: + type: string + description: Configuration prompt for the assistant + largeModelParameters: + type: object + description: Parameters for the large language model + required: + - model + - parameters + properties: + model: + type: string + example: "gpt-4" + parameters: + type: object + required: + - temperature + - max_tokens + properties: + temperature: + type: number + format: float + minimum: 0.0 + maximum: 1.0 + example: 0.7 + max_tokens: + type: integer + minimum: 1 + example: 200 + top_p: + type: number + format: float + minimum: 0.0 + maximum: 1.0 + example: 0.8 + openingRemarks: + type: string + description: Optional opening remarks for the assistant + + AssistantUpdateRequest: + type: object + properties: + name: + type: string + description: New name of the assistant + description: + type: string + description: New description of the assistant + knowledgeBaseId: + type: string + description: Optional new knowledge base ID + configurationPrompt: + type: string + description: Updated configuration prompt + largeModelParameters: + type: object + description: Updated model parameters + properties: + model: + type: string + parameters: + type: object + properties: + temperature: + type: number + format: float + max_tokens: + type: integer + top_p: + type: number + format: float + openingRemarks: + type: string + description: Updated opening remarks + + Assistant: + type: object + properties: + assistantId: + type: string + description: Unique identifier of the assistant + format: uuid + example: "a1b2c3d4-5678-90ab-cdef-1234567890ab" + name: + type: string + description: + type: string + knowledgeBaseId: + type: string + configurationPrompt: + type: string + largeModelParameters: + type: object + properties: + model: + type: string + parameters: + type: object + openingRemarks: + type: string + createdAt: + type: string + format: date-time + updatedAt: + type: string + format: date-time + + AssistantResponse: + type: object + properties: + success: + type: boolean + description: Whether the operation succeeded + assistantId: + type: string + description: Unique identifier of the assistant + format: uuid + message: + type: string + description: Success/failure message + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - MISSING_REQUIRED_PARAM + - INVALID_PARAMETER_VALUE + - INVALID_ARGUMENT + examples: + GENERIC_400_MISSING_REQUIRED_PARAM: + description: Missing required parameter + value: + status: 400 + code: MISSING_REQUIRED_PARAM + message: "Required parameter 'configurationPrompt' is missing" + GENERIC_400_INVALID_PARAMETER_VALUE: + description: Invalid parameter value + value: + status: 400 + code: INVALID_PARAMETER_VALUE + message: "Temperature must be between 0.0 and 1.0" + GENERIC_400_INVALID_ARGUMENT: + description: Invalid argument + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions for this operation + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Token context inconsistency + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "Assistant ID is not consistent with access token" + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ASSISTANT_NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_ASSISTANT_NOT_FOUND: + description: Assistant not found + value: + status: 404 + code: ASSISTANT_NOT_FOUND + message: "Specified assistant ID does not exist" + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Assistant identifier not found. + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + - INTERNAL + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred" + GENERIC_500_INTERNAL: + description: Internal server error + value: + status: 500 + code: INTERNAL + message: Unknown server error diff --git a/original/ModelAsAService/code/API_definitions/qa-assistant-service.yaml b/original/ModelAsAService/code/API_definitions/qa-assistant-service.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e6286f876cf1a3e18e8844f382a75cd6596660f0 --- /dev/null +++ b/original/ModelAsAService/code/API_definitions/qa-assistant-service.yaml @@ -0,0 +1,363 @@ +openapi: 3.0.3 +info: + title: Q&A Assistant - Service + description: >- + This API provides service interfaces for the Question and Answer (Q&A) Assistant, enabling users to submit query requests to a configured Q&A assistant and obtain answers generated based on the knowledge base and Large Language Model (LLM). + It is suitable for scenarios such as building intelligent question-answering systems and customer service bots that require real-time responses to user inquiries. + It must follow RFC 3339 and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ. + + ## Security and Authentication + + This API uses OAuth 2.0 with OpenID Connect for authentication. The following scope is required: + - qa-assistant-service:answer:read - Permission to query assistants + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ModelAsAService + +servers: + - url: '{apiRoot}/qa-assistant-service/v0.1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +paths: + /answer: + post: + operationId: queryAssistant + summary: Get an answer from a QA assistant + description: | + Queries a configured QA assistant to generate answers using knowledge bases and LLMs. + + **Key Features:** + - Utilizes pre-configured assistant settings (prompts, model parameters) + - Leverages associated knowledge bases for contextual responses + - Provides termination status for answer generation + + **Key Rules:** + - Requires valid UUID `assistantId` + - `prompt` must be 1-1000 characters + - Needs `qa-assistant-service:answer:read` scope + - Assistant must be properly configured and accessible + + **Response Characteristics:** + - **200 OK**: Returns `QueryResponse` with answer text and termination status + - `finished` indicates generation completion reason (Stop/Length/Error/Filter) + - `reference` shows knowledge base source when available + - **400 Bad Request**: + - Missing/invalid prompt + - Invalid assistantId format + - Prompt length exceeds limits + - **401 Unauthenticated**: Missing/invalid credentials + - **403 Forbidden**: + - Missing required scope + - Token/assistantId mismatch + - **404 Not Found**: + - Assistant doesn't exist + - Identifier not found + - **500 Internal Server Error**: + - LLM processing failure + - Knowledge base access error + tags: + - Query + parameters: + - $ref: '#/components/parameters/x-correlator' # Added correlator + security: + - openId: + - qa-assistant-service:answer:read + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/QueryRequest' + responses: + '200': + description: Successful answer retrieval + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/QueryResponse' + '400': + $ref: '#/components/responses/Generic400' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + description: OpenID Connect authentication + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for request tracing + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + QueryRequest: + type: object + required: + - assistantId + - prompt + properties: + assistantId: + type: string + format: uuid + description: Unique identifier of the QA assistant + example: "a1b2c3d4-5678-90ab-cdef-1234567890ab" + prompt: + type: string + minLength: 1 + maxLength: 1000 + description: The user's question or query + example: "How do I reset my password?" + + QueryResponse: + type: object + required: + - success + - finished + - answerText + properties: + success: + type: boolean + description: Indicates whether the query was processed successfully + finished: + type: string + description: Termination status of the response generation + enum: + - Stop + - Length + - Error + - Filter + example: "Stop" + answerText: + type: string + description: The assistant's generated answer + example: "To reset your password, go to settings > security..." + reference: + type: string + description: Optional reference to the knowledge base source + example: "kb123_section5" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code + code: + type: string + description: Error code identifier + message: + type: string + description: Human-readable error message + + responses: + Generic400: + description: Bad request due to invalid input + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - MISSING_PROMPT + - INVALID_ASSISTANT_ID + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_MISSING_PROMPT: + description: Missing required prompt parameter + value: + status: 400 + code: MISSING_PROMPT + message: "Required parameter 'prompt' is missing" + GENERIC_400_INVALID_ASSISTANT_ID: + description: Invalid assistant ID format + value: + status: 400 + code: INVALID_ASSISTANT_ID + message: "Assistant ID must be a valid UUID" + GENERIC_400_INVALID_ARGUMENT: + description: Invalid argument + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument" + GENERIC_400_OUT_OF_RANGE: + description: Parameter value out of range + value: + status: 400 + code: OUT_OF_RANGE + message: "Prompt length exceeds maximum allowed characters" + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: User lacks required permissions + value: + status: 403 + code: PERMISSION_DENIED + message: User lacks required permissions to query this assistant + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Token context inconsistency + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "Assistant ID is not consistent with access token" + + Generic404: + description: Resource not found + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - ASSISTANT_NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_ASSISTANT_NOT_FOUND: + description: Assistant not found + value: + status: 404 + code: ASSISTANT_NOT_FOUND + message: "Specified assistant ID does not exist" + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Assistant identifier not found. + + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: '#/components/parameters/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + - INTERNAL + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Unexpected server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: "Unexpected server error occurred while processing query" + GENERIC_500_INTERNAL: + description: Internal server error + value: + status: 500 + code: INTERNAL + message: Unknown server error diff --git a/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..4f1dec9035955bf853982e6bfc7bd321508b3b2a --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md @@ -0,0 +1,10 @@ +# Model as a Service - Knowledge Base User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a standardized API to create, manage, and populate knowledge bases with documents, so that I can build knowledge-intensive applications (like intelligent customer service or enterprise wikis) with fine-grained access control and full traceability. | +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server)
                                                    **Actors:** Application Service Provider, End-Users interacting with the knowledge-based application.
                                                    **Scope:** Full CRUD (Create, Read, Update, Delete) lifecycle management of knowledge base resources and document upload.| +| ***Pre-conditions*** |
                                                    • The API Consumer (application server) is onboarded to the CSP's API platform.
                                                    • The API Consumer has successfully subscribed to the Knowledge Base API product.
                                                    • The API Consumer has obtained a valid OAuth 2.0 access token with the required scopes for the intended operation (e.g., knowledge-base:knowledge-bases:create).
                                                    | +| ***Activities/Steps*** |Starts when: The API Consumer application server makes an authenticated API request (e.g., POST /knowledge-bases to create a new knowledge base).
                                                    Ends when: The requested operation is completed by the API server and a success or error response is received (e.g., 201 Created for a successful creation). | +| ***Post-conditions*** |The state of the knowledge base system is changed according to the operation (e.g., a new knowledge base is created and available, a document is added to a knowledge base, a knowledge base is deleted). The API consumer can proceed with its application logic. | +| ***Exceptions*** |
                                                    • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope.
                                                    • 400 Bad Request: Invalid input (e.g., missing required 'name' field, invalid document format).
                                                    • 404 Not Found: Referenced resource (e.g., knowledgeBaseId) does not exist.
                                                    • 415 Unsupported Media Type: Attempting to upload a document type not supported (e.g., not doc, pdf, txt, csv).
                                                    • 500 Internal Server Error: An unexpected error occurred on the server during processing.
                                                    | diff --git a/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..80d8074734cf1ca61eb42c381392a579a63d755d --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md @@ -0,0 +1,10 @@ +# Model as a Service - Knowledge Base and Q&A Assistant User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application development lead at a financial services company, I need to leverage a comprehensive set of knowledge management and intelligent Q&A APIs to transform our extensive financial product documentation, compliance guidelines, and customer service manuals into a smart Q&A system. This will enable our clients to quickly obtain accurate product information and compliance advice through natural language queries, while our customer service team can handle complex inquiries more efficiently. Ultimately, this will enhance customer satisfaction and reduce operational costs.| +| ***Roles, Actor(s) and scope*** |**Actors:**
                                                    • Financial Services Company:Development Lead - Decides on API integration and leads the development team
                                                    • Financial Services Company:Development Team - Implements API integration
                                                    • Financial Services Company:Customer Service Manager - Defines knowledge base content and Q&A requirements
                                                    • Financial Services Company:Compliance Officer - Ensures content meets regulatory requirements
                                                    • End Customer - End-user utilizing the intelligent Q&A functionality
                                                    • Customer Service Representative - Uses the system to assist customer service
                                                    • Communication Service Provider (CSP) - Provides the API platform and services

                                                    **Scope:**
                                                    • Creation and management of multiple knowledge bases (e.g., "Investment Products," "Loan Services," "Compliance Guidelines")
                                                    • Upload of documents in various formats (PDF product brochures, DOCX compliance documents, TXT FAQs, CSV data sheets)
                                                    • Configuration of dedicated Q&A assistants for different scenarios (e.g., "Investment Advisor Assistant," "Loan Specialist Assistant")
                                                    • Adjustment of large language model parameters to optimize answer quality and style
                                                    • API queries to obtain intelligent answers based on the knowledge base
                                                    • Tracking answer sources to ensure compliance and auditability| +| ***Pre-conditions*** |The following prerequisites must be met:
                                                    1. Financial Services Company:Development Lead has evaluated and selected the CSP's API solution, and Customer Service Manager and Compliance Officer have confirmed requirements
                                                    2. The company has subscribed to the Knowledge Base and Q&A Assistant API product package through the CSP's business portal
                                                    3. Development Team has registered the company application on the CSP platform and obtained necessary credentials (e.g., client ID and secret)
                                                    4. The company backend system has implemented the OAuth 2.0 client flow and can obtain access tokens with required scopes (e.g., knowledge-base:knowledge-bases:create, qa-assistant-service:answer:read)
                                                    5. Compliance Officer has reviewed and approved the data processing plan to ensure compliance with financial industry regulations (e.g., GDPR, PCI DSS)| +| ***Activities/Steps*** |**Starts when:** The company decides to implement an intelligent Q&A system to improve customer service quality

                                                    **Typical implementation and usage process:**
                                                    1. Knowledge Base Planning - Customer Service Manager and Compliance Officer jointly determine the scope and categorization of documents to be digitized
                                                    2. Knowledge Base Creation - Development Team calls POST /knowledge-bases to create structured knowledge bases like "Investment Products" and "Loan Services"
                                                    3. Document Upload - Use POST /knowledge-bases/{id}/documents to batch upload documents such as product brochures and compliance files
                                                    4. Assistant Configuration - Create Q&A assistants for different scenarios via POST /assistants, setting specialized configurationPrompt to ensure answers comply with financial industry standards
                                                    5. Model Tuning - Adjust largeModelParameters such as temperature and max_tokens based on Customer Service Manager feedback to balance answer creativity and accuracy
                                                    6. System Integration - Integrate the Q&A API (POST /answer) into the company website, mobile apps, and customer service workstation
                                                    7. Customer Query - End Customer asks questions through company channels, and the system uses the appropriate assistantId and user question as prompt to call the API
                                                    8. Answer Generation - CSP service returns a response containing answerText and reference, ensuring answers are traceable to knowledge base sources
                                                    9. Continuous Optimization - Regularly update knowledge base content and assistant configurations based on user feedback and customer service usage

                                                    **Ends when:** The customer receives accurate, helpful answers, and all interactions comply with regulatory requirements| +| ***Post-conditions*** |• The company maintains a continuously updated digital knowledge base containing all important financial product and compliance documentation
                                                    • Multiple dedicated Q&A assistants are configured and capable of handling customer queries across different domains
                                                    • Customers can quickly obtain accurate financial information through natural language without navigating complex documents
                                                    • Customer service representatives can use the system to quickly respond to complex inquiries, improving work efficiency
                                                    • All Q&A interactions are recorded and traceable to sources, meeting financial industry compliance and audit requirements
                                                    • The system can be easily expanded as business grows, adding new knowledge bases and assistants| +| ***Exceptions*** |Potential exceptions and handling methods:

                                                    • 401 Unauthorized/403 Forbidden - Invalid access token or insufficient permissions (e.g., attempting to upload documents with read-only token). The system should reacquire a valid token or prompt the administrator to adjust permissions
                                                    • 400 Bad Request - Input parameters do not meet requirements (e.g., missing knowledge base name, prompt exceeding 1000 characters, temperature parameter outside 0.0-1.0 range). Should validate inputs and provide clear error messages
                                                    • 404 Not Found - Requested resource does not exist (e.g., using incorrect knowledge base ID or assistant ID). Should verify the correctness of resource identifiers
                                                    • 415 Unsupported Media Type - Attempting to upload unsupported file formats. Should restrict upload file types and validate in advance
                                                    • 500 Internal Server Error - Server-side processing error (e.g., LLM processing failure, document parsing error). Should log error details and implement retry mechanisms, while notifying administrators
                                                    • Insufficient Answer Quality - Generated answers are inaccurate or incomplete. Should optimize by improving prompt engineering, adjusting model parameters, or enhancing knowledge base content
                                                    • Response Delay - Q&A response time is too long, affecting user experience. Should consider implementing asynchronous processing or caching common answers
                                                    • Compliance Risks - Answer content may involve compliance issues. Should establish manual review processes and content filtering mechanisms to ensure compliance with financial regulations| diff --git a/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..e6e6de7ced0775aabf2878d87e6aede25ad7eb20 --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md @@ -0,0 +1,10 @@ +# Model as a Service - Q&A Assistant Manage User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a standardized API to create, configure, and manage intelligent Q&A assistants based on Large Language Models (LLMs), so that I can build customizable intelligent customer service or question-answering systems with fine-grained control over model behavior, knowledge sources, and prompting strategies. | +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server)
                                                    **Actors:** Application Service Provider, End-Users interacting with the Q&A service.
                                                    **Scope:** Full CRUD (Create, Read, Update, Delete) lifecycle management of Q&A assistant configurations, including LLM parameter tuning, knowledge base association, and prompt engineering.| +| ***Pre-conditions*** |
                                                    • The API Consumer (application server) is onboarded to the CSP's API platform.
                                                    • The API Consumer has successfully subscribed to the Q&A Assistant Management API product.
                                                    • The API Consumer has obtained a valid OAuth 2.0 access token with the required scopes for the intended operation (e.g., qa-assistant-manage:assistants:create).
                                                    | +| ***Activities/Steps*** |**Starts when:** The API Consumer application server makes an authenticated API request (e.g., POST /assistants to create a new assistant with specified LLM parameters and prompts).
                                                    **Ends when:** The requested operation is completed by the API server and a success or error response is received (e.g., 201 Created with a generated assistantId).| +| ***Post-conditions*** |The state of the Q&A assistant system is changed according to the operation (e.g., a new assistant configuration is created and available, an existing assistant's parameters are updated). The API consumer can use the configured assistant for intelligent question-answering.| +| ***Exceptions*** |
                                                    • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope; token context inconsistency.
                                                    • 400 Bad Request: Invalid input (e.g., missing required parameters like name or configurationPrompt, parameter values like temperature outside allowed range 0.0-1.0).
                                                    • 404 Not Found: Referenced resource (e.g., assistantId) does not exist.
                                                    • 500 Internal Server Error: An unexpected error occurred on the server during processing (e.g., assistant creation or update failure).
                                                    | diff --git a/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..8173f420e13116e2c698cab6d0acfeb8edb4f0a4 --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md @@ -0,0 +1,10 @@ +# Model as a Service - Q&A Assistant Service User Story + +| Item | Description | +|---------------------------|-------------| +| ***Summary*** |As an application developer, I want to use a service API to submit user queries to a pre-configured Q&A assistant, so that I can integrate intelligent, knowledge-based question-answering capabilities into my applications, providing real-time responses to end-user inquiries through LLM-powered assistants.| +| ***Roles, Actor(s) and scope*** |**Roles:** Application Developer, API Consumer (Application Server), End-User
                                                    **Actors:** Application Service Provider, End-Users submitting queries.
                                                    **Scope:** Submitting query requests to configured assistants and retrieving generated answers based on knowledge bases and LLM configurations.| +| ***Pre-conditions*** |
                                                    • The API Consumer (application server) is onboarded to the CSP's API platform.
                                                    • The API Consumer has successfully subscribed to the Q&A Assistant Service API product.
                                                    • A Q&A assistant has been previously configured and is accessible via its assistantId.
                                                    • The API Consumer has obtained a valid OAuth 2.0 access token with the required qa-assistant-service:answer:read scope.
                                                    | +| ***Activities/Steps*** |**Starts when:** The API Consumer application server makes an authenticated POST request to /answer with a valid assistantId and a user prompt (1-1000 characters).
                                                    **Ends when:** The API server processes the query using the configured assistant and knowledge base, then returns a response containing the generated answer and termination status.| +| ***Post-conditions*** |The end-user receives an intelligent response to their query. The API response includes the generated answer text, completion status (finished field indicating Stop/Length/Error/Filter), and optional knowledge base reference. The application can display this answer to the user.| +| ***Exceptions*** |
                                                    • 400 Bad Request: Missing or invalid parameters (e.g., missing prompt, invalid UUID format for assistantId, prompt length exceeds 1000 characters).
                                                    • 401/403 Unauthorized/Forbidden: Invalid, missing, or expired access token; lack of required OAuth scope; token/assistantId context mismatch.
                                                    • 404 Not Found: The specified assistantId does not exist or is not accessible.
                                                    • 500 Internal Server Error: Backend processing failure (e.g., LLM processing error, knowledge base access issue).
                                                    | diff --git a/original/ModelAsAService/documentation/API_documentation/README.MD b/original/ModelAsAService/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist.md b/original/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ca269431e6fc572100ee038eb2744cb72699e3ad --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/knowledge-base-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for knowledge-base v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [knowledge-base.yaml](/code/API_definitions/knowledge-base.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_knowledge_base_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md),| +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/original/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist.md b/original/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..7c261f9c773d7d779cc665ada8049b42efc19e97 --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/qa-assistant-manage-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qa-assistant-manage v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qa-assistant-manage.yaml](/code/API_definitions/qa-assistant-manage.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_qa_assistant_manage_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md)| +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/original/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist.md b/original/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..f70e200cb8770c49f4e5b7e7f2fa0cf1ee46027d --- /dev/null +++ b/original/ModelAsAService/documentation/API_documentation/qa-assistant-service-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qa-assistant-service v0.1.0 in r1.2. + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qa-assistant-service.yaml](/code/API_definitions/qa-assistant-service.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [for a single API](/documentation/API_documentation/ModelAsAService_qa_assistant_service_User_Story.md), [leveraging multiple APIs](/documentation/API_documentation/ModelAsAService_knowledge_base_and_qa_assistant_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N/A | This is the first public release | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/fgLWB) | diff --git a/original/ModelAsAService/documentation/SupportingDocuments/README.MD b/original/ModelAsAService/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ModelAsAService/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/MostFrequentLocation/README.md b/original/MostFrequentLocation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..c409cf056951e06de3abedf01454e643753519eb --- /dev/null +++ b/original/MostFrequentLocation/README.md @@ -0,0 +1,54 @@ + + + + + + + + + +# MostFrequentLocation + +Sandbox API Repository to describe, develop, document, and test the MostFrequentLocation Service API(s). The repository does not yet belong to a CAMARA Sub Project, but works together with DeviceVisitLocation as Location Insights. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XjPe) + +## Scope + +* Service APIs for “MostFrequentLocation” (see APIBacklog.md) +* It provides the API Consumer with the ability to: + * "MostFrequentLocation": validate, in terms of scoring, of the user's expected home area + * NOTE: The scope of these APIs should be limited (at least at the first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/MostFrequentLocation/releases/tag/r2.2) (Fall25), with the following API versions: + * **most-frequent-location v0.2.0** + [[YAML]](https://github.com/camaraproject/MostFrequentLocation/blob/r2.2/code/API_definitions/most-frequent-location.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/MostFrequentLocation/r2.2/code/API_definitions/most-frequent-location.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/MostFrequentLocation/r2.2/code/API_definitions/most-frequent-location.yaml) +* The latest public release is always available here: https://github.com/camaraproject/MostFrequentLocation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/MostFrequentLocation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/MostFrequentLocation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: On-demand + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/99479758031?password=c705dd6f-a1c5-44e4-af97-331a18395fb8) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564467/MostFrequentLocation+2024+Minutes) + * Slack channel: [camara-project.slack.com](https://camara-project.slack.com/archives/C07BHCZ3XUY) #sp-location-insights +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/MostFrequentLocation/code/API_definitions/most-frequent-location.yaml b/original/MostFrequentLocation/code/API_definitions/most-frequent-location.yaml new file mode 100644 index 0000000000000000000000000000000000000000..d0bd9d3add8c8692811fdf88a7f4ae539d3f76b9 --- /dev/null +++ b/original/MostFrequentLocation/code/API_definitions/most-frequent-location.yaml @@ -0,0 +1,586 @@ +openapi: 3.0.3 +info: + title: Most Frequent Location + description: | + The Most Frequent Location API provides API Consumers with the ability to verify the frequency of a device's location within a specific geographic area. + + # Introduction + + This API verifies if a device is present most of the time in a certain location. This location insight is useful as an approach to the residence location of the end-user. + + This API can be used in anti-fraud cases where an application provider needs further evidence about the reported place of residence of the end-user. Also, for service provision or personalization tasks when the service provider needs to manage their offer depending on the habits of the end-user. + + Such use cases are transversal to different sectors such as: + + - Financial institutions: to mitigate risks about identity fraud, helping in their compliance with AML/KYC regulation. + - Insurance companies: to assess risks and prevent fraudulent claims. + - E-commerce and retail: to ensure accurate shipping and delivery, fraud prevention and targeted marketing. + - Digital Content Delivery companies: to verify service provisioning and billing, and to comply with regulation. + - Utilities: to verify service provisioning and billing, and to prevent service theft. + - Real estate: to screen potential tenants and ensure that lease agreements are in compliance with local laws. + + # Relevant terms and definitions + + * **Device**: End-user equipment able to connect to a network. Examples of devices include smartphones, home gateways or IoT sensors/actuators. + + * **Geographical reference**: Using coordinates or a reference code, the geographical surface where a device can be physically located is specified. + + * **Verification**: The process triggered on the API server to calculate the frequency of time a device is at a given location. + + # API functionality + + The API allows API Consumers to verify the frequency with which a device is in a specific location. The location can be specified using a geographical reference of type: + - `COVERAGE_ZONE`: It is specified by latitude and longitude coordinates. The coverage area is generated by one or more antennas closest to the specified coordinates, determining the device's connection to these antennas. + - `POSTAL_CODE`: A zip code or postal code that delimits a geographic area. + + The operation returns a score representing how frequently the device was connected to antennas whose coverage cover the requested area in certain time slots. The range of score values is between "0" and "100", where higher scores indicate a more frequent presence in the location. + + The `score` value maps to the frequency as follows: + - `score = 0`: The device has never been in the specified location. + - `score = 100`: The device is almost always in the specified location. + + ## Identifying a device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ## Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ## Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.2.0 + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/MostFrequentLocation +servers: + - url: "{apiRoot}/most-frequent-location/v0.2" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Frequent location verification + description: Verification of the most frequent location of a device +paths: + /verify: + post: + security: + - openId: + - most-frequent-location:verify + tags: + - Frequent location verification + summary: Verify the most frequent location of a device + description: |- + Verify the frequency with which a device is within a requested geographic area location. The location can be defined by a postal code or a latitude and longitude coordinates. The operation returns a score representing how frequently the device was connected to antennas whose coverage covers the requested area. + operationId: verifyFrequentLocation + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Request body with a device as identifier and geographical reference for location + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyFrequentLocationRequest' + examples: + INPUT_PHONE_NUMBER_POSTAL_CODE: + summary: Phone number and postal code + description: Verify the frequency with which the device, identified by a phone number, has been in a location delimited by a postal code + value: + device: + phoneNumber: '+123456789' + geoReference: + type: POSTAL_CODE + postalCode: '12345' + INPUT_PHONE_NUMBER_COVERAGE_ZONE: + summary: Phone number and coverage zone + description: Verify the frequency with which the device, identified by a phone number, has been in a location delimited by a coverage zone specified by latitude and longitude coordinates + value: + device: + phoneNumber: '+123456789' + geoReference: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + INPUT_IP_ADDRESS_V4_POSTAL_CODE: + summary: IPv4 address and postal code + description: Verify the frequency with which the device, identified by an IPv4 address, has been in a location delimited by a postal code + value: + device: + ipv4Address: + publicAddress: '123.234.1.2' + publicPort: 1234 + geoReference: + type: POSTAL_CODE + postalCode: '12345' + INPUT_IP_ADDRESS_V4_COVERAGE_ZONE: + summary: IPv4 address and coverage zone + description: Verify the frequency with which the device, identified by an IPv4 address, has been in a location delimited by a coverage zone specified by latitude and longitude coordinates + value: + device: + ipv4Address: + publicAddress: '123.234.1.2' + publicPort: 1234 + geoReference: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + responses: + '200': + description: Most frequent location verification result + content: + application/json: + schema: + $ref: '#/components/schemas/VerifyFrequentLocationResponse' + examples: + HIGH_SCORE: + summary: High score with detail + description: The device has been at the requested location with high frequency for most of the time. + value: + score: 86 + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/VerifyFrequentLocationBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/VerifyFrequentLocationPermissionDenied403' + '404': + $ref: '#/components/responses/VerifyFrequentLocationNotFound404' + '422': + $ref: '#/components/responses/VerifyFrequentLocationUnprocessableEntity422' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + schemas: + VerifyFrequentLocationRequest: + type: object + description: Request with a device as identifier and geographical reference for location + required: + - geoReference + properties: + device: + $ref: '#/components/schemas/Device' + geoReference: + $ref: '#/components/schemas/GeoReference' + VerifyFrequentLocationResponse: + type: object + description: Calculated Score Response + required: + - score + properties: + score: + $ref: '#/components/schemas/Score' + Device: + description: |- + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + networkAccessIdentifier: + $ref: '#/components/schemas/NetworkAccessIdentifier' + ipv4Address: + $ref: '#/components/schemas/DeviceIpv4Addr' + ipv6Address: + $ref: '#/components/schemas/DeviceIpv6Address' + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access + identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: 123456789@domain.com + DeviceIpv4Addr: + type: object + description: |- + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: '#/components/schemas/SingleIpv4Addr' + privateAddress: + $ref: '#/components/schemas/SingleIpv4Addr' + publicPort: + $ref: '#/components/schemas/Port' + anyOf: + - required: + - publicAddress + - privateAddress + - required: + - publicAddress + - publicPort + example: + publicAddress: 84.125.93.10 + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: 84.125.93.10 + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: |- + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + GeoReference: + description: |- + Specific Geographical reference. It can be defined in different ways, such as by a postal code or coverage zone specified by latitude and longitude coordinates. + type: object + properties: + type: + $ref: '#/components/schemas/GeoReferenceType' + required: + - type + discriminator: + propertyName: type + mapping: + COVERAGE_ZONE: '#/components/schemas/CoverageZone' + POSTAL_CODE: '#/components/schemas/PostalCode' + GeoReferenceType: + type: string + description: |- + Type of this geographical reference. + - `COVERAGE_ZONE`: It is specified by latitude and longitude coordinates. The coverage area is generated by one or more antennas closest to the specified coordinates, determining the device's connection to these antennas. + - `POSTAL_CODE`: A zip code or postal code that delimits a geographic area. + enum: + - COVERAGE_ZONE + - POSTAL_CODE + CoverageZone: + description: Coverage zone specified by latitude and longitude coordinates + allOf: + - $ref: '#/components/schemas/GeoReference' + - type: object + properties: + latitude: + $ref: '#/components/schemas/Latitude' + longitude: + $ref: '#/components/schemas/Longitude' + example: + latitude: 50.735851 + longitude: 7.10066 + required: + - latitude + - longitude + example: + type: COVERAGE_ZONE + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + example: 50.735851 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + example: 7.10066 + PostalCode: + description: Area associated to an administrative or geographical code + allOf: + - $ref: '#/components/schemas/GeoReference' + - type: object + properties: + postalCode: + type: string + description: Zip code or postal code. + required: + - postalCode + Score: + type: integer + description: |- + The value is a summary metric derived from analysis of the device's connections to antennas covering the requested area across all time slots. + The range of score values is between "0" and "100", where higher scores indicate a more frequent presence in the location. + minimum: 0 + maximum: 100 + example: 86 + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represent + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + responses: + VerifyFrequentLocationBadRequest400: + description: |- + Bad Request. + In addition to regular scenario of `INVALID_ARGUMENT`, other scenarios may exist: + + - Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested ("code": "OUT_OF_RANGE","message": "Client specified an invalid range.") + - The postal code value does not exist or is invalid ("code": "MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID","message": "Requested postal code value does not exist or is invalid."). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + POSTAL_CODE_NOT_VALID: + description: The postal code value does not exist or is invalid + value: + status: 400 + code: MOST_FREQUENT_LOCATION.POSTAL_CODE_NOT_VALID + message: Requested postal code value does not exist or is invalid. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + VerifyFrequentLocationPermissionDenied403: + description: |- + Forbidden. + In addition to regular scenario of `PERMISSION_DENIED`, another scenarios may exist: + + - Phone number cannot be deducted from access token context.("code": "INVALID_TOKEN_CONTEXT","message": "Phone number is not consistent with access token.") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + VerifyFrequentLocationNotFound404: + description: |- + Not found. + In addition to regular scenario of `NOT_FOUND`, other scenarios may exist: + + - Device identifier not found ("code": "IDENTIFIER_NOT_FOUND","message": "Device identifier not found."). + - There is not enough information to calculate the score ("code": "MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE","message": "Requested information is not available"). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + - MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + INFORMATION_NOT_AVAILABLE: + description: There is not enough information to calculate the score + value: + status: 404 + code: MOST_FREQUENT_LOCATION.INFORMATION_NOT_AVAILABLE + message: Requested information is not available. + VerifyFrequentLocationUnprocessableEntity422: + description: |- + Unprocessable Content. + + - Service is not available for the provided device ("code": "SERVICE_NOT_APPLICABLE","message": "The service is not available for the provided device."). + - None of the provided device identifiers are supported by the implementation ("code": "UNSUPPORTED_IDENTIFIER","message": "Supported device identifiers are: ..."). + - The device identifier is not included in the request and the device information cannot be derived from the 3-legged access token ("code": "MISSING_IDENTIFIER","message": "The device cannot be identified."). + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" diff --git a/original/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist.md b/original/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..bd0acd0f390bb7a133c12987c0e784d5570970f3 --- /dev/null +++ b/original/MostFrequentLocation/documentation/API_documentation/most-frequent-location-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for most-frequent-location v0.2.0 in release r2.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                                                    initial | public-release
                                                    stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/most-frequent-location.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/most-frequent-location.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/most-frequent-location-check.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/most-frequent-location-check.feature) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/G4LVB) | + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). \ No newline at end of file diff --git a/original/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations.md b/original/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations.md new file mode 100644 index 0000000000000000000000000000000000000000..376011a7987edc108a5c61fbee5cd7107b7c0375 --- /dev/null +++ b/original/MostFrequentLocation/documentation/SupportingDocuments/postalCodeConsiderations.md @@ -0,0 +1,30 @@ +# Most Frequent Location API + +## Considerations about 'postalCode' and Country Name + +This document consolidates the discussion of the issue https://github.com/camaraproject/MostFrequentLocation/issues/7 + +### Problem description +Postal code is not globally unique. For example, 31000 is Pamplona in Spain and Toulouse in France. In most cases the country can be derived from the phone number, but there can be other more sophisticated cases. +Making postal code unique should help to detect error API calls. + +### Assumptions to solve and simplify the problem + +**Actors**: Application service provider (ASP), ASP:User, End-User, Communication Service Provider (CSP). + +**Assumptions**: +1. The End-User has a valid contract with a CSP in a specific country. +2. The CSP calculates the most frequent location insight of an End-User for that country where the CSP provides the service to the End-User. +3. The CSP can't provide the most frequent location insight for a country different from that of the contract. +4. The Application Service Provider User (ASP:User) wants to verify the most frequent location of the End-User using the 'phoneNumber' parameter of the API, which includes the country prefix. +6. The ASP:User assumes that the most frequent location insight is calculated for the country referred by the country prefix of the MSISDN. + +**Under these assumptions, the MFL API will return the insight expected by the ASP:User, and no additional parameter, such as 'countryName' is needed.** + +Any usage of the API out of these assumptions could provide misleading responses. For example, corner cases related with roaming, federation, or even coincident postal codes. + +## Other considerations + +If a common definition related to 'postalCode' is eventually specified at https://github.com/camaraproject/Commonalities, it will be reviewed for the evolution of this API. + +The only related issue so far does not consider 'postalCode': https://github.com/camaraproject/Commonalities/pull/315 \ No newline at end of file diff --git a/original/MultiPointVPN/README.md b/original/MultiPointVPN/README.md new file mode 100644 index 0000000000000000000000000000000000000000..5a7bd4833d9e31390c17228bd7287b4fab364ace --- /dev/null +++ b/original/MultiPointVPN/README.md @@ -0,0 +1,41 @@ + + + + + + + + + +# MultiPointVPN + +Sandbox API Repository to describe, develop, document, and test the MultiPointVPN Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYD7Bw) + +## Scope + +* Service API(s) “MultiPointVPN” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * The MultiPoint VPN API transforms the process of ordering private or customized network services across multiple touchpoints. It enables users to create and configure on-demand edge connectivity services with guaranteed SLA and bandwidth with just one click, eliminating the need for manual orders through phone calls or customer managers. When the API is called with specific network SLA requirements, telecom operators can create non-public cloud leased network services by orchestrating IP VPN connections across various networks, including data centers, private clouds, operator networks, and satellite links +* Describe, develop, document, and test the API(s) +* Started: June 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly meeting on Wednesday every 2 week(s), at 12:30 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/AYD7Bw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/MultiPointVPN/code/API_definitions/README.MD b/original/MultiPointVPN/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/MultiPointVPN/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/MultiPointVPN/code/API_definitions/multi-point-vpn.yaml b/original/MultiPointVPN/code/API_definitions/multi-point-vpn.yaml new file mode 100644 index 0000000000000000000000000000000000000000..4a8709164157cb3d98aadfefac64df0033afb8cd --- /dev/null +++ b/original/MultiPointVPN/code/API_definitions/multi-point-vpn.yaml @@ -0,0 +1,634 @@ +openapi: 3.0.3 +info: + title: MultiPoint Virtual Private Network + description: > + ##### Before starting to use the API, the developer needs to know about the + below specified details : + + * Multipoint VPN service endpoint The URL pointing to the RESTful resource of the Multipoint VPN API. + + * Authentication Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the Multipoint VPN API. + + * Identifier for access point Customer Edge (CE) IPv4 addressand/or IPv6 address of the Customer Edge Router. + + * Identifier for the endpoint cloud Provider Edge (PE) IPv4 and/or IPv6 address of the Cloud Provider Edge. + + * Identifier for the application server(AS)IPv4 and/or IPv6 address of the application server (cloud virtual machine). + + * App-Flow (between the application client and application server). The developer wants to have non public network delivery for the precise application data flow for the application users. + + * Duration Duration (in hours) for which the Multipoint VPN session (between CE and cloud PE) should be created. This parameter is optional. + When not specified, a default session duration (e.g. 6 months) is applied. The user may request a termination before its expiration. + + * Physical Location Physical location of the Customer Edge Router. + + NOTE- The private physical link between CE and cloud PE is default deployed for one click calling, + otherwise it is required to install the physical link, which is out of the scope of this API. + version: wip + license: + name: Apache 2.0 + url: 'https://www.apache.org/licenses/LICENSE-2.0.html' + x-camara-commonalities: 0.5 +externalDocs: + description: Project documentation at CAMARA + url: 'https://github.com/camaraproject/MultiPointVPN' +servers: + - url: '{apiRoot}/multipointvpn/vwip' + variables: + apiRoot: + default: 'http://localhost:9091' + description: API root +tags: + - name: Network Assessment + description: Operations to manage Multipoint VPN connection assessments + - name: Network + description: Operations to manage Multipoint VPN connection +paths: + /network: + post: + tags: + - Network + summary: To create a multipoint virtual private network + description: Create a multipoint virtual private network + operationId: createNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkCreate" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionRequest" + responses: + "201": + description: CreateVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + /network/{serviceId}: + patch: + tags: + - Network + summary: To update a multipoint virtual private network + description: Update a new multipoint virtual private network + operationId: updateNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/NetworkUpdate" + examples: + SITE_TO_CLOUD_VPN_UPDATE_CONNECTION: + $ref: "#/components/examples/siteToCloudVPNUpdateConnectionRequest" + responses: + "200": + description: UpdateVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + get: + tags: + - Network + summary: retrieve multipoint virtual private network details + description: Retrieve multipoint virtual private network details + operationId: getVPNConnect + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + responses: + "200": + description: getNetworkDetails + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Connection" + examples: + SITE_TO_CLOUD_VPN_CREATE_CONNECTION_RESPONSE: + $ref: "#/components/examples/siteToCloudVPNCreateConnectionResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + delete: + tags: + - Network + summary: Delete multipoint virtual private network + description: Delete multipoint virtual private network + operationId: deleteNetwork + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/serviceId' + responses: + "202": + description: deleteVPNConnectionResponse + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + /assessment: + post: + tags: + - Network Assessment + summary: Assess Multipoint VPN connection feasibility + description: Get the feasibility assessment for a Multipoint VPN connection + operationId: assessConnectionFeasibility + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/AssessmentRequest" + examples: + SITE_TO_CLOUD_VPN_ASSESSMENT: + $ref: "#/components/examples/siteToCloudVPNFeasibilityAssessmentRequest" + responses: + "200": + description: Assessment result + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssessmentResult" + examples: + SITE_TO_CLOUD_VPN_ASSESSMENT_RESULT: + $ref: "#/components/examples/siteToCloudVPNFeasibilityAssessmentResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" +components: + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{0,55}$ + serviceId: + name: serviceId + required: true + schema: + type: string + in: path + description: Identifier of the Resource + schemas: + Amount: + type: object + description: An amount in a given unit + properties: + amount: + type: number + format: float + default: 1 + description: Numeric value in a given unit + currency: + type: string + description: currency + AssessmentRequest: + description: Base schema for all areas + type: object + properties: + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + $ref: '#/components/schemas/Duration' + AssessmentResult: + type: object + properties: + waitdays: + type: integer + description: the waiting-days until the vpn can be offered + minimum: 1 + sla: + type: string + enum: + - A + - AA + - AAA + rent: + $ref: '#/components/schemas/Amount' + Connection: + allOf: + - type: object + description: Another Characteristic that is related to the current Characteristic; + properties: + id: + type: string + description: Unique identifier for the connection + customerEdge: + $ref: '#/components/schemas/EdgeConnection' + providerEdge: + $ref: '#/components/schemas/EdgeConnection' + Duration: + type: object + description: Guarantee duration + properties: + value: + type: number + format: float + default: 1 + description: Numeric value in a given unit + unit: + type: string + description: unit + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + EdgeConnection: + description: Edge connection details + type: object + properties: + type: + description: Multipoint VPN access point type + enum: + - site + - cloud + primaryIpAddress: + $ref: '#/components/schemas/IpAddress' + secondaryIpAddress: + $ref: '#/components/schemas/IpAddress' + location: + type: string + description: connection location + IpAddress: + type: object + properties: + addressType: + type: string + required: + - addressType + discriminator: + propertyName: addressType + mappings: + - Ipv4Addr: '#/components/schemas/Ipv4Address' + - Ipv6Addr: '#/components/schemas/Ipv6Address' + Ipv4Address: + allOf: + - $ref: '#/components/schemas/IpAddress' + - type: object + required: + - address + properties: + address: + type: string + format: ipv4 + Ipv6Address: + allOf: + - $ref: '#/components/schemas/IpAddress' + - type: object + required: + - address + properties: + address: + type: string + format: ipv6 + Network: + description: Base Network Entity structure + type: object + properties: + serviceId: + type: string + description: unique id for network service + serviceName: + type: string + description: vpn service name + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + sla: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + $ref: '#/components/schemas/Duration' + routeProtocal: + type: string + resourceGroupId: + type: string + cloudGatewayIP: + type: string + NetworkCreate: + description: Base Connection Entity structure + type: object + properties: + serviceName: + type: string + description: vpn service name + isProtected: + type: boolean + description: Is Multipoint VPN protected + connections: + type: array + items: + $ref: '#/components/schemas/Connection' + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + sla: + type: string + enum: + - A + - AA + - AAA + duration: + $ref: '#/components/schemas/Duration' + routeProtocal: + type: string + NetworkUpdate: + description: Base Connection Entity structure + type: object + properties: + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + sla: + type: string + enum: + - A + - AA + - AAA + + examples: + siteToCloudVPNFeasibilityAssessmentRequest: + summary: Assesment Sample 1 + description: Feasibility assessment sample + value: + isProtected: true + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + guaranteeBandwidth: 20 + duration: + value: 6 + unit: days + + siteToCloudVPNFeasibilityAssessmentResponse: + summary: Assesment Sample 1 + description: Feasibility assessment sample + value: + waitdays: 1 + sla: A + rent: + amount: 2000 + currency: GBP + siteToCloudVPNCreateConnectionRequest: + summary: Create Connection Sample 1 + description: Create Connection request sample + value: + isProtected: true + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + guaranteeBandwidth: 20 + duration: + value: 6 + unit: days + + siteToCloudVPNCreateConnectionResponse: + summary: Create Connection Sampl 1 + description: Create Connection response sample + value: + serviceId: 111111 + connections: + - customerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + location: string + providerEdge: + type: site + primaryIP: 84.125.93.10 + secondaryIP: 84.125.94.10 + resourceGroupId: 12121 + cloudGatewayIP: 1.2.3.4 + siteToCloudVPNUpdateConnectionRequest: + summary: Update Connection Sample 1 + description: Update Connection request sample + value: + serviceId: 111111 + guaranteeBandwidth: 10 + sla: A + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic500: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL_SERVER_ERROR + examples: + GENERIC_500_INTERNAL_SERVER_ERROR: + description: Internal server error + value: + status: 500 + code: INTERNAL_SERVER_ERROR + message: Internal server error while processing request. diff --git a/original/MultiPointVPN/documentation/API_documentation/README.MD b/original/MultiPointVPN/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/MultiPointVPN/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/MultiPointVPN/documentation/SupportingDocuments/README.MD b/original/MultiPointVPN/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/MultiPointVPN/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/NetworkAccessManagement/README.md b/original/NetworkAccessManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..357ca41be24b0bccbb9dbd2d5d147cd5f037321b --- /dev/null +++ b/original/NetworkAccessManagement/README.md @@ -0,0 +1,38 @@ + + + + + + + + + +# NetworkAccessManagement + +Sandbox API Repository to describe, develop, document, and test the NetworkAccessManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/5wCzHQ) + +## Scope +* Service APIs for “Network Access Management” of Home Devices (see APIBacklog.md) +* It provides the customer with the ability to: + * manage fixed devices provided by network operators that reside at customer premises. +* Describe, develop, document, and test the APIs (with 1-2 Telcos) +* Started: May 2024 + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96846363178?password=9ebebe6c-c59c-42be-a709-7d5fd42fb626) + * Schedule: Bi-weekly on Fridays at 8AM MDT / 4PM CEST + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/ez3e). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/NetworkAccessManagement/code/API_definitions/README.md b/original/NetworkAccessManagement/code/API_definitions/README.md new file mode 100644 index 0000000000000000000000000000000000000000..9fca112d0a8f999433a8acf57dd2193d79748e6f --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/README.md @@ -0,0 +1,199 @@ +# Network Access Management API Definitions + +This directory contains the OpenAPI specifications for the Network Access Management API, organized into modular components for better maintainability and reusability. + +## Overview + +The API definitions have been restructured from a monolithic approach to a modular, component-based architecture. This allows for better code reuse, easier maintenance, and cleaner separation of concerns. + +## Folder Structure + +``` +API_definitions/ +├── README.md # This file (authoring & process docs) +├── redocly.yaml # Lint/bundle configuration (Redocly CLI) +├── network-access-management.yaml # Source API spec with $ref references (committed on main) +├── common/ +│ └── CAMARA_common.yaml # Shared CAMARA-style error responses +└── modules/ # Modular domain-focused component files + ├── NAM_Common.yaml # Shared primitives (UUID, DateTime, ResourceAudit, securitySchemes) + ├── AccessDetail.yaml # Discriminated access detail variants (Wi-Fi, Thread) + ├── Capabilities.yaml # Device capability schemas + ├── Policy.yaml # Trust Domain policy schemas (maxDevices, bandwidth, egress) + ├── NetworkAccessDevices/ # Network Access Device resource schemas + ├── RebootRequests/ # Reboot Request lifecycle schemas + ├── Services/ # Service and ServiceSite schemas + └── TrustDomains/ # Trust Domain & related capability schemas +``` + +## Architecture Rationale + +### Why Multiple Files? + +**Before:** Single monolithic OpenAPI file (`network-access-management.yaml`) +- ✅ Simple to understand initially +- ❌ Became very large (2000+ lines) +- ❌ Hard to maintain and review +- ❌ Schema duplication across different APIs +- ❌ Merge conflicts in collaborative development +- ❌ No reusability between different API specifications + +**After:** Modular component-based structure +- ✅ Each file has a single, clear responsibility +- ✅ Reusable schemas can be shared across APIs +- ✅ Easier to review and maintain individual components +- ✅ Parallel development by different team members +- ✅ Clear separation of concerns +- ✅ Smaller, focused files + +### Component Breakdown + +| File | Purpose | Reusability | +|------|---------|-------------| +| `Common.yaml` | Base types (UUID, DateTime, ErrorInfo) | High - used across all APIs | +| `Policy.yaml` | Trust Domain governance policies | Medium - Trust Domain specific | +| `AccessDetail.yaml` | Network access configurations | Medium - Network-related APIs | +| `TrustDomains.yaml` | Core Trust Domain schemas | Low - Trust Domain specific | + +## Bundling and Validation + +### Key Constraint: Bundled Files Are Not Committed on Main + +Per the [CAMARA Consumption and Bundling Design](https://github.com/camaraproject/Commonalities/blob/main/documentation/Commonalities-Consumption-and-Bundling-Design.md), **bundled (standalone) API definitions are never committed on `main`**. The committed `network-access-management.yaml` retains its `$ref` references to `common/` and `modules/`. Bundled standalone OAS files are produced only on release branches/tags and for local validation. + +This avoids merge conflicts in the large bundled output and keeps `main` as the single source of truth for modular schema authoring. + +Bundled output files (`*-bundled.yaml`) are listed in `.gitignore`. + +### Prerequisites + +Install Redocly CLI: +```bash +npm install -g @redocly/cli +``` + +### Linting + +Validate the spec and all referenced modules resolve correctly: +```bash +cd code/API_definitions +redocly lint network-access-management.yaml +``` + +### Local Bundling (for Validation or Tooling) + +To produce a fully resolved, standalone OAS file locally: +```bash +cd code/API_definitions +redocly bundle network-access-management.yaml --output network-access-management-bundled.yaml +``` + +The bundled file is useful for: +- Importing into API tools (Swagger UI, Postman, etc.) +- Validating the fully resolved spec with external validators +- Generating SDKs or documentation locally + +**Do not commit `*-bundled.yaml` files to `main`.** They are git-ignored. + +### Bundling Configuration + +The `redocly.yaml` file contains: +- **Linting rules** - Ensures consistency and quality +- **File resolution** - Allows `.yaml` and `.yml` extensions + +Key bundling features: +- Resolves all `$ref` references to external files +- Validates schema compatibility +- Generates self-contained OpenAPI specifications +- Preserves examples and documentation + +## File Purposes + +### API Specification + +- **`network-access-management.yaml`** - Source API specification with `$ref` references to `common/` and `modules/`. This is the file committed on `main`. Bundling resolves these refs into a standalone OAS file for release branches and local tooling. + +### Component Files + +- **`common/CAMARA_common.yaml`** - Shared CAMARA-style error responses and common schemas +- **`modules/NAM_Common.yaml`** - Shared fundamental types (UUID, DateTime, ResourceAudit, securitySchemes) +- **`modules/Policy.yaml`** - Trust Domain policy schemas (maxDevices, bandwidth limits, egress rules) +- **`modules/AccessDetail.yaml`** - Network access configuration schemas (Wi-Fi, Thread, security modes) +- **`modules/Capabilities.yaml`** - Device capability schemas +- **`modules/TrustDomains/TrustDomains.yaml`** - Core Trust Domain schemas and examples +- **`modules/NetworkAccessDevices/NetworkAccessDevices.yaml`** - Network Access Device resource schemas +- **`modules/RebootRequests/RebootRequests.yaml`** - Reboot Request lifecycle schemas +- **`modules/Services/Services.yaml`** - Service schemas +- **`modules/Services/ServiceSites.yaml`** - Service Site schemas + +## Best Practices + +### When to Create New Component Files +- **High reusability** - Schemas used by multiple APIs +- **Logical grouping** - Related schemas that form a cohesive unit +- **Size management** - When a file exceeds ~500 lines + +### Schema Design Guidelines +- Use `$ref` for external schema references +- Keep examples close to their schemas +- Use YAML anchors for internal reuse within files +- Document inheritance and discriminator patterns clearly + +### Example Cross-Reference Limitations + +**Important:** While schemas can be easily shared across files using `$ref`, examples have significant limitations in the distributed component model: + +#### The Problem +```yaml +# ❌ This does NOT work - cannot use $ref inside example values +TrustDomainExample: + summary: Trust Domain with Wi-Fi access + value: + name: "My Network" + accessDetails: + - $ref: "modules/AccessDetail.yaml#/components/examples/WiFiExample/value" # Invalid! +``` + +#### The Solutions + +**Option 1: Local Example Duplication (Recommended)** +```yaml +# ✅ Define examples locally where they're used +TrustDomainExample: + summary: Trust Domain with Wi-Fi access + value: + name: "My Network" + accessDetails: + - accessType: "Wi-Fi" + ssid: "my-network" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" +``` + +**Option 2: YAML Anchors (Within Same File Only)** +```yaml +# ✅ Use anchors for reuse within the same file +_wifi_example: &wifi-access + accessType: "Wi-Fi" + ssid: "my-network" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + +components: + examples: + TrustDomainExample: + value: + accessDetails: + - *wifi-access # Reuse within same file +``` + +**Option 3: Component-Level Example References** +```yaml +# ✅ Reference complete examples at component level (not within values) +WiFiAccessExample: + $ref: "modules/AccessDetail.yaml#/components/examples/WiFiAccessDetailWPA2Personal" + +# But you still can't compose these inside other example values +``` diff --git a/original/NetworkAccessManagement/code/API_definitions/common/CAMARA_common.yaml b/original/NetworkAccessManagement/code/API_definitions/common/CAMARA_common.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f5df4ab72d5a30dc7e95111c91391255051ce403 --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/common/CAMARA_common.yaml @@ -0,0 +1,771 @@ +# This file was pulled from https://github.com/camaraproject/Commonalities/blob/r3.4/artifacts/CAMARA_common.yaml +# in order to reference Commonalities models directly from spec files using $ref statements. +# +# IMPORTANT: This file has been modified in this repo in order to address linter warnings/errors that +# occurred in examples that referenced generic placeholder values like {{SPECIFIC_CODE}} or {{SPECIFIC_CODE_MESSAGE}}. +# The original file was using { { SPECIFIC_CODE } } in examples which had two issues. First, it's not quoted so it +# conform to the enum type (string). Second, even when quoted, the extraneous spaces inside the curly braces made it +# not conform to the pattern defined for that field. The modifications made were to remove any such placeholder entries +# from the examples, while leaving the rest of the example intact. +openapi: 3.0.3 +info: + title: CAMARA common data types + description: Common data types for CAMARA APIs + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.7.1 + x-camara-commonalities: 0.6 + +paths: {} +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + required: + - startDate + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + responses: + ####################################################### + ####################################################### + # ERROR RESPONSE SCHEMA TEMPLATE + # - Objective: Make normative error `status` and `code` values + # - Schema Template rationale: + # - The `allOf` in content.application/json.schema allows a combination of both the generic ErrorInfo schema and the specific schema for this error response, + # which validates that `status` and `code` have only the specified values. + # This `allOf` is used without discriminator because it does not imply any hierarchy between the models, just 2 schemas that must be independently validated. + ####################################################### + # ErrorResponseSchema: + # ... + # content: + # application/json: + # schema: + # allOf: + # - $ref: '#/components/schemas/ErrorInfo' + # - type: object + # properties: + # status: + # enum: + # - + # code: + # enum: + # - + # - + # examples: + # ExampleKey1: + # value: + # status: + # code: + # message: + # ExampleKey2: + # value: + # status: + # code: + # message: + ####################################################### + ####################################################### + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 405 + code: + enum: + - METHOD_NOT_ALLOWED + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 406 + code: + enum: + - NOT_ACCEPTABLE + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by the client through `Accept-*` headers. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic412: + description: Failed precondition + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 412 + code: + enum: + - FAILED_PRECONDITION + examples: + GENERIC_412_FAILED_PRECONDITION: + description: Indication by the API Server that the request cannot be processed in current system state + value: + status: 412 + code: FAILED_PRECONDITION + message: Request cannot be executed in the current system state. + Generic415: + description: Unsupported Media Type + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 415 + code: + enum: + - UNSUPPORTED_MEDIA_TYPE + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Payload format of the request is in an unsupported format by the Server. Should not happen + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 500 + code: + enum: + - INTERNAL + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - NOT_IMPLEMENTED + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as far as possible to get the objective to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 502 + code: + enum: + - BAD_GATEWAY + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 503 + code: + enum: + - UNAVAILABLE + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 504 + code: + enum: + - TIMEOUT + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. diff --git a/original/NetworkAccessManagement/code/API_definitions/modules/AccessDetail.yaml b/original/NetworkAccessManagement/code/API_definitions/modules/AccessDetail.yaml new file mode 100644 index 0000000000000000000000000000000000000000..09e06b9baae95e60e2d04efa3bf6f1071930f65c --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/modules/AccessDetail.yaml @@ -0,0 +1,225 @@ +# This file defines the AccessDetail schema model for different network access types. +# It includes Wi-Fi and Thread access details with various security modes. + +components: + schemas: + # Base security mode schemas (unchanged) + WpaPersonalDetail: + type: object + description: WPA Personal security mode configuration for Wi-Fi networks. + properties: + password: + type: string + writeOnly: true + minLength: 8 + maxLength: 255 + pattern: "^[\\x20-\\x7E]{8,63}$" + description: The password for the WPA Personal Wi-Fi network + example: &wpa-personal-password "my-password" + securityModeType: + type: string + enum: + - WPA2-Personal + - WPA2-WPA3-Personal + - WPA3-Personal + description: | + The security mode type for the WPA Personal Wi-Fi network. + Leave blank to auto-select. + example: &wpa-personal-security-mode-type "WPA3-Personal" + additionalProperties: false + required: + - password + example: &wpa-personal + password: *wpa-personal-password + securityModeType: *wpa-personal-security-mode-type + + WpaEnterpriseDetail: + type: object + description: WPA Enterprise security mode configuration for Wi-Fi networks. + properties: + authServer: + type: string + maxLength: 255 + description: The authentication server for the WPA Enterprise Wi-Fi network + example: &wpa-enterprise-auth-server "1.2.3.4" + securityModeType: + type: string + enum: + - WPA2-Enterprise + - WPA3-Enterprise + description: The security mode type for the WPA Enterprise Wi-Fi network + example: &wpa-enterprise-security-mode-type "WPA3-Enterprise" + additionalProperties: false + required: + - securityModeType + example: &wpa-enterprise + authServer: *wpa-enterprise-auth-server + securityModeType: *wpa-enterprise-security-mode-type + + # Flattened concrete implementations for Wi-Fi + WiFiWpaPersonalAccessDetail: + type: object + description: Complete access details for Wi-Fi networks using WPA Personal security mode. + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_PERSONAL" + example: "Wi-Fi:WPA_PERSONAL" + ssid: + type: string + minLength: 2 + maxLength: 32 + pattern: "^(?! )[\\x20-\\x7E]{2,32}(?- + List of devices to reboot. When undefined, the reboot targets the 'default' device (simple use case that + wouldn't use locations or devices). Throws an error when creating if there is no 'default' device. + example: *device-id-list + + RebootRequest: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceIdentifier" + - $ref: "#/components/schemas/RebootRequestCreate" + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceAudit" + - type: object + properties: + id: + readOnly: true + createdAt: + readOnly: true + createdBy: + readOnly: true + modifiedAt: + readOnly: true + modifiedBy: + readOnly: true + required: + - devices + description: Represents a reboot request for one or more network access devices. + + RebootRequestList: + type: array + items: + $ref: "#/components/schemas/RebootRequest" + + examples: + RebootRequestCreateImmediateDefaultDevice: + summary: Example of a Reboot Request for immediate reboot + value: + message: "reboot to correct performance" + + RebootRequestCreateScheduledMultipleDevices: + summary: Example of a Reboot Request for scheduled reboot of multiple devices + value: + message: "Scheduled reboot for maintenance" + atTime: *date-time + devices: *device-id-list + + RebootRequestResponseInferred: + summary: Response after inferred default device reboot request + value: + id: *uuid-example-1 + message: "reboot to correct performance" + devices: + - *device-uuid-1 + atTime: *date-time + createdAt: *date-time + createdBy: *created-by-example + modifiedAt: *date-time + modifiedBy: *modified-by-example + + RebootRequestResponseExplicit: + summary: Response after explicit multi-device reboot request + value: + id: *uuid-example-2 + message: "scheduled maintenance reboot" + devices: *device-id-list + atTime: *date-time + createdAt: *date-time + createdBy: *created-by-example + modifiedAt: *date-time + modifiedBy: *modified-by-example diff --git a/original/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites.yaml b/original/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites.yaml new file mode 100644 index 0000000000000000000000000000000000000000..1274a306e3363b15211d1c228aa7023f636a7721 --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/modules/Services/ServiceSites.yaml @@ -0,0 +1,67 @@ +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + uuid-example-2: &uuid-example-2 "123e4567-e89b-12d3-a456-426614174000" + property-address-example: &property-address-example + id: *uuid-example + addressLine1: "123 Main St" + addressLine2: "Suite 456" + streetNr: "123" + streetNrSuffix: "A" + streetNrLast: "125" + streetNrLastSuffix: "B" + streetName: "Main" + subUnitType: "Apartment" + subUnitNr: "A12" + levelType: "Floor" + levelNr: "3" + buildingName: "Sunset Towers" + privateStreetName: "Private Rd" + locality: "Example Locality" + city: "Example State" + stateOrProvince: "EX" + country: "United States" + postCode: "12345" + postCodeExtension: "6789" + +components: + schemas: + ServiceSite: + type: object + description: A Service Site represents a subscriber location associated with one or more Network Access Devices. Implementations MAY provide geographic coordinates, postal address data, or both, depending on local regulatory and operational requirements. + properties: + id: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/UUID" + readOnly: true + name: + type: string + description: The name of the service site. + maxLength: 64 + example: &service-site-name "Example Service Site 1" + description: + type: string + description: A textual description of the service site. + maxLength: 64 + example: &service-site-description "This is the first example service site" + location: + type: object + description: Geographic location information for the service site, including coordinates and/or property address. + properties: + geographicPoint: + $ref: "../../common/CAMARA_common.yaml#/components/schemas/Point" + propertyAddress: + $ref: "../NAM_Common.yaml#/components/schemas/PropertyAddress" + example: &service-site-location + geographicPoint: + latitude: 50.735851 + longitude: 7.10066 + propertyAddress: *property-address-example + required: + - id + example: &service-site + id: *uuid-example + name: *service-site-name + description: *service-site-description + location: *service-site-location diff --git a/original/NetworkAccessManagement/code/API_definitions/modules/Services/Services.yaml b/original/NetworkAccessManagement/code/API_definitions/modules/Services/Services.yaml new file mode 100644 index 0000000000000000000000000000000000000000..3d7c2524dbb7b5343b7e4d607d87af048f8a538a --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/modules/Services/Services.yaml @@ -0,0 +1,101 @@ +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + uuid-example-2: &uuid-example-2 "123e4567-e89b-12d3-a456-426614174000" + uuid-example-3: &uuid-example-3 "123e4567-e89b-12d3-a456-426614174001" + property-address-example: &property-address-example + id: *uuid-example + addressLine1: "123 Main St" + addressLine2: "Suite 456" + streetNr: "123" + streetNrSuffix: "A" + streetNrLast: "125" + streetNrLastSuffix: "B" + streetName: "Main" + subUnitType: "Apartment" + subUnitNr: "A12" + levelType: "Floor" + levelNr: "3" + buildingName: "Sunset Towers" + privateStreetName: "Private Rd" + locality: "Example Locality" + city: "Example State" + stateOrProvince: "EX" + country: "United States" + postCode: "12345" + postCodeExtension: "6789" + service-site-example: &service-site-example + id: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + name: "Primary Residence" + description: "123 Main Street" + location: *property-address-example + +components: + parameters: + serviceId: + name: serviceId + in: path + description: The unique identifier of the Service. If the service exists but the caller lacks permission to access it, the API returns 403. + required: true + schema: + $ref: "#/components/schemas/ServiceId" + + schemas: + ServiceId: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/UUID" + description: | + A unique identifier that represents a service account associated with this resource. + + Must be a valid UUID as defined by RFC 4122 (versions 1-5) using only lowercase hexadecimal characters. + + Service: + type: object + description: | + A service represents a logical commercial subscription or account relationship + between a network operator and a subscriber. This may correspond to residential, + commercial, public Wi-Fi, or other service types. + properties: + id: + $ref: "#/components/schemas/ServiceId" + name: + type: string + maxLength: 64 + description: Optional friendly name for the service + example: "Main Home Internet" + description: + type: string + maxLength: 255 + description: Optional description of the service + example: "Internet subscription for primary residence" + serviceSite: + # Optional. Present for location-specific services (e.g., residential, office), absent for general services (e.g., public Wi-Fi) + $ref: "./ServiceSites.yaml#/components/schemas/ServiceSite" + required: + - id + example: + id: *uuid-example + name: "Main Home Internet" + description: "Internet subscription for primary residence" + serviceSite: + id: *uuid-example-2 + name: "Primary Residence" + description: "123 Main Street" + + ServiceList: + type: array + description: A list of services accessible to the calling identity + items: + $ref: "#/components/schemas/Service" + example: + - id: *uuid-example + name: "Main Home Internet" + description: "Internet subscription for primary residence" + serviceSite: + id: *uuid-example-2 + name: "Primary Residence" + description: "123 Main Street" + - id: *uuid-example-3 + name: "Vacation Home Internet" + description: "Internet subscription for vacation home" diff --git a/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities.yaml b/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities.yaml new file mode 100644 index 0000000000000000000000000000000000000000..4d180cd763e994fdfc6155942ebebc3b5debedc2 --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomainCapabilities.yaml @@ -0,0 +1,280 @@ +components: + schemas: + TrustDomainCapabilities: + type: object + properties: + supportedAccessTypes: + type: array + description: List of supported access types and their variants + items: + $ref: "#/components/schemas/SupportedAccessType" + minItems: 1 + supportedPolicies: + type: object + description: Map of supported policy types to their capability details + properties: + maxDevices: + $ref: "#/components/schemas/MaxDevicesPolicyCapability" + maxDomainDownstreamRate: + $ref: "#/components/schemas/BandwidthPolicyCapability" + maxDomainUpstreamRate: + $ref: "#/components/schemas/BandwidthPolicyCapability" + egressAllowedList: + $ref: "#/components/schemas/EgressPolicyCapability" + example: + maxDevices: + maxValue: 100 + minValue: 1 + maxDomainDownstreamRate: + maxValue: 1000000000 + minValue: 1000000 + required: + - supportedAccessTypes + description: Describes the Trust Domain configuration capabilities supported by this API provider + + SupportedAccessType: + type: object + description: Access type capabilities with discriminated properties based on accessType. Represents the configuration options supported by the API provider for a given access type. This is distinct from AccessDetail, which represents the configuration requested by an API client. + properties: + accessType: + type: string + enum: + - "Wi-Fi:WPA_PERSONAL" + - "Wi-Fi:WPA_ENTERPRISE" + - "Thread:STRUCTURED" + - "Thread:TLV" + description: The supported access type identifier (must match POST endpoint values) + oneOf: + - $ref: "#/components/schemas/SupportedWiFiWpaPersonalAccessType" + - $ref: "#/components/schemas/SupportedWiFiWpaEnterpriseAccessType" + - $ref: "#/components/schemas/SupportedThreadStructuredAccessType" + - $ref: "#/components/schemas/SupportedThreadTlvAccessType" + discriminator: + propertyName: accessType + mapping: + "Wi-Fi:WPA_PERSONAL": "#/components/schemas/SupportedWiFiWpaPersonalAccessType" + "Wi-Fi:WPA_ENTERPRISE": "#/components/schemas/SupportedWiFiWpaEnterpriseAccessType" + "Thread:STRUCTURED": "#/components/schemas/SupportedThreadStructuredAccessType" + "Thread:TLV": "#/components/schemas/SupportedThreadTlvAccessType" + required: + - accessType + + SupportedWiFiWpaPersonalAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_PERSONAL" + example: "Wi-Fi:WPA_PERSONAL" + wifiProperties: + $ref: "#/components/schemas/WiFiAccessTypeProperties" + required: + - accessType + - wifiProperties + description: Wi-Fi WPA Personal access type capabilities + + SupportedWiFiWpaEnterpriseAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Wi-Fi:WPA_ENTERPRISE" + example: "Wi-Fi:WPA_ENTERPRISE" + wifiProperties: + $ref: "#/components/schemas/WiFiAccessTypeProperties" + required: + - accessType + - wifiProperties + description: Wi-Fi WPA Enterprise access type capabilities + + SupportedThreadStructuredAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Thread:STRUCTURED" + example: "Thread:STRUCTURED" + threadProperties: + $ref: "#/components/schemas/ThreadAccessTypeProperties" + required: + - accessType + - threadProperties + description: Thread structured access type capabilities + + SupportedThreadTlvAccessType: + type: object + properties: + accessType: + type: string + description: The type of network access. + enum: + - "Thread:TLV" + example: "Thread:TLV" + threadProperties: + $ref: "#/components/schemas/ThreadAccessTypeProperties" + required: + - accessType + - threadProperties + description: Thread TLV access type capabilities + + # Explicit policy capability schemas + MaxDevicesPolicyCapability: + type: object + properties: + maxValue: + type: integer + minimum: 1 + description: Maximum number of devices allowed + example: 100 + minValue: + type: integer + minimum: 1 + description: Minimum number of devices allowed + example: 1 + required: + - maxValue + - minValue + description: Capabilities for maximum devices policy + + BandwidthPolicyCapability: + type: object + properties: + maxValue: + type: integer + minimum: 1 + description: Maximum bandwidth value in bits per second + example: 1000000000 + minValue: + type: integer + minimum: 1 + description: Minimum bandwidth value in bits per second + example: 1000000 + required: + - maxValue + - minValue + description: Capabilities for bandwidth control policies + + EgressPolicyCapability: + type: object + properties: + maxEntries: + type: integer + minimum: 1 + description: Maximum number of allowed egress destinations + example: 50 + supportedDestinationTypes: + type: array + items: + type: string + enum: ["IP", "FQDN", "CIDR"] + description: Supported destination address formats + example: ["IP", "FQDN", "CIDR"] + required: + - maxEntries + - supportedDestinationTypes + description: Capabilities for egress allowed list policy + + # Explicit access type property schemas + WiFiAccessTypeProperties: + type: object + properties: + ssidRequired: + type: boolean + description: Whether SSID must be provided (false if can be inferred) + example: true + supportedSecurityModes: + type: array + items: + type: string + enum: + - "WPA2-Personal" + - "WPA3-Personal" + - "WPA2-WPA3-Personal" + - "WPA2-Enterprise" + - "WPA3-Enterprise" + description: Supported Wi-Fi security mode types + example: ["WPA2-Personal", "WPA3-Personal"] + passwordConstraints: + $ref: "#/components/schemas/PasswordConstraints" + authServerRequired: + type: boolean + description: Whether authentication server must be specified for Enterprise modes + example: false + description: Wi-Fi specific access type properties + + ThreadAccessTypeProperties: + type: object + properties: + supportedChannels: + type: object + properties: + min: + type: integer + minimum: 11 + maximum: 26 + description: Minimum supported Thread channel + example: 11 + max: + type: integer + minimum: 11 + maximum: 26 + description: Maximum supported Thread channel + example: 26 + required: + - min + - max + description: Range of supported Thread channels + networkKeyFormat: + type: string + enum: ["32-hex-digits"] + description: Required format for Thread network keys + example: "32-hex-digits" + networkNameConstraints: + type: object + properties: + minLength: + type: integer + minimum: 1 + example: 1 + maxLength: + type: integer + minimum: 1 + example: 16 + required: + - minLength + - maxLength + description: Constraints on Thread network names + maxDatasetLength: + type: integer + minimum: 1 + description: Maximum length for TLV operational dataset (applies to Thread:TLV) + example: 255 + description: Thread specific access type properties + + PasswordConstraints: + type: object + properties: + minLength: + type: integer + minimum: 8 + description: Minimum password length + example: 8 + maxLength: + type: integer + minimum: 1 + description: Maximum password length + example: 63 + requireSpecialCharacters: + type: boolean + description: Whether special characters are required + example: false + required: + - minLength + - maxLength + description: Password validation constraints diff --git a/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains.yaml b/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains.yaml new file mode 100644 index 0000000000000000000000000000000000000000..d45da43db377939b192bf7ce1ddc6123dbe86d4d --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/modules/TrustDomains/TrustDomains.yaml @@ -0,0 +1,265 @@ +# Local anchor definitions for external component examples. There isn't a native OpenAPI way to +# cross-reference examples across files, so we define them here for reuse. +_imported_examples: + uuid-example: &uuid-example "3fa85f64-5717-4562-b3fc-2c963f66afa6" + service-uuid-example: &service-uuid-example "123e4567-e89b-12d3-a456-426614174000" + wifi-wpa2-personal-basic-example: &wifi-wpa2-personal-basic-example + accessType: "Wi-Fi:WPA_PERSONAL" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + + wifi-wpa2-personal-example: &wifi-wpa2-personal-example + accessType: "Wi-Fi:WPA_PERSONAL" + ssid: "my-ssid" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + + wifi-wpa3-personal-example: &wifi-wpa3-personal-example + accessType: "Wi-Fi:WPA_PERSONAL" + ssid: "my-ssid" + securityMode: + password: "my-password" + securityModeType: "WPA3-Personal" + + thread-structured-example: &thread-structured-example + accessType: "Thread:STRUCTURED" + channel: 13 + extendedPanId: "d63e8e3e495ebbc3" + networkKey: "dfd34f0f05cad978ec4e32b0413038ff" + networkName: "Spec-Thread-B3AF" + panId: "d63e" + + thread-tlv-example: &thread-tlv-example + accessType: "Thread:TLV" + mode: tlv + operationalDataset: "0e08000000000000010010000102030405060708090a0b0c0d0e0f" + + max-devices-policy-example: &max-devices-policy-example + maxDevices: 10 + + max-bandwidth-policy-example: &max-bandwidth-policy-example + maxDomainDownstreamRate: + value: 1000000 + unit: Kbps + maxDomainUpstreamRate: + value: 500000 + unit: Kbps + + egress-allowed-list-policy-example: &egress-allowed-list-policy-example + egressAllowedList: + - "api.vendor.com" + - "updates.vendor.com" + + created-by-example: &created-by-example "550e8400-e29b-41d4-a716-446655440000" + modified-by-example: &modified-by-example "660e8400-e29b-41d4-a716-446655440000" + modified-by-example-2: &modified-by-example-2 "770e8400-e29b-41d4-a716-446655440000" + +components: + + parameters: + trustDomainId: + name: trustDomainId + in: path + required: true + schema: + $ref: "../NAM_Common.yaml#/components/schemas/UUID" + description: ID of the Trust Domain. If the Trust Domain exists but the caller lacks permission to access it, the API returns 403. + + schemas: + + TrustDomainUpdate: + type: object + description: Represents the updatable fields of a trust domain within the network access management system. + properties: + name: + type: string + description: Human-readable name for the trust domain. + example: "Primary WiFi Network" + description: + type: string + description: Detailed description of the trust domain. + example: "Primary home WiFi Network for all devices" + enabled: + type: boolean + description: Indicates whether the trust domain is currently enabled. + example: true + expiration: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/DateTime" + - description: | + The expiration date and time of the network. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows + 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z). + + If omitted, the trust domain will not automatically expire. + policies: + $ref: "../Policy.yaml#/components/schemas/Policies" + accessDetails: + type: array + # Each item grants access for a device to this Trust Domain, scoped by the associated AP/network access device or AP group. + description: | + A list of access configurations that define how end-user devices may join the + Trust Domain. Each entry represents one access type (e.g., Wi-Fi WPA Personal, + Wi-Fi WPA Enterprise, Thread Structured, Thread TLV). + + **Multiplicity and Uniqueness** + - A Trust Domain MUST contain at least one accessDetail entry. + - Each `accessType` SHOULD appear at most once. If multiple entries of the same + `accessType` are provided, the API provider MAY reject the request. + - Order of entries has no semantic meaning. + + **Creation and Update Semantics** + - On creation (POST), the full list of accessDetails MUST be provided. + - On update (PATCH), the list replaces the previous list entirely when included. + Partial merge semantics are not defined; clients MUST supply the complete + desired configuration for this field. + - To remove all access types, clients MAY provide an empty array, although the + API provider MAY reject configurations that result in no valid admittance + method for the Trust Domain. + + **Validation Expectations** + - The API provider MUST validate that the requested access types and their + properties conform to the provider's advertised capabilities + (via GET /trust-domains/capabilities). + - Providers MAY enforce additional constraints (e.g., SSID uniqueness, + channel restrictions, Thread dataset rules) based on local policy. + + **Deployment Behavior** + - All Network Access Devices configured with this Trust Domain MUST apply all + supplied accessDetails entries, unless the provider's capabilities indicate + that certain access types are not supported on specific devices. + items: + $ref: "../AccessDetail.yaml#/components/schemas/AccessDetail" + minItems: 1 + + TrustDomainCreate: + allOf: + - $ref: "#/components/schemas/TrustDomainUpdate" + description: Represents the creation of a new trust domain within the network access management system. + required: + - name + - enabled + - accessDetails + - serviceId + properties: + serviceId: + $ref: "../Services/Services.yaml#/components/schemas/ServiceId" + + TrustDomain: + allOf: + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceIdentifier" + - $ref: "#/components/schemas/TrustDomainCreate" + - $ref: "../NAM_Common.yaml#/components/schemas/ResourceAudit" + - type: object + properties: + id: + readOnly: true + createdAt: + readOnly: true + createdBy: + readOnly: true + modifiedAt: + readOnly: true + modifiedBy: + readOnly: true + description: Represents a trust domain within the network access management system. + + + examples: + + TrustDomainCreateWpa2Personal: + summary: Create a Trust Domain with WPA2-Personal Wi-Fi access. + value: + name: "Primary WiFi Network" + description: "Request defines a Trust Domain with WPA2-Personal Wi-Fi access. The request specifies an SSID, implying the SSID is created on the network infrastructure." + enabled: true + accessDetails: + - <<: *wifi-wpa2-personal-example + serviceId: *service-uuid-example + + TrustDomainCreateInferredSsid: + summary: Create a Trust Domain with inferred SSID Wi-Fi access. + value: + name: "Inferred SSID Network" + description: "Request defines a Trust Domain with inferred SSID Wi-Fi access. The request omits the SSID, implying the Trust Domain is applied to an existing SSID on the network infrastructure." + enabled: true + accessDetails: + - accessType: "Wi-Fi:WPA_PERSONAL" + securityMode: + password: "my-password" + securityModeType: "WPA2-Personal" + serviceId: *service-uuid-example + + TrustDomainCreateEphemeral: + summary: Create a Trust Domain with ephemeral access details. + value: + name: "Ephemeral Network" + description: "Request defines a Trust Domain with ephemeral access details." + enabled: true + accessDetails: + - <<: *wifi-wpa3-personal-example + expiration: "2024-12-31T23:59:59Z" + policies: + <<: *max-devices-policy-example + serviceId: *service-uuid-example + + TrustDomainCreateThreadStructured: + summary: Create a Trust Domain with Thread structured access details. + value: + name: "Thread Structured Network" + description: "Request defines a Trust Domain with Thread structured access details." + enabled: true + accessDetails: + - <<: *thread-structured-example + serviceId: *service-uuid-example + + TrustDomainCreateQoSPolicies: + summary: Create a Trust Domain with QoS policies. + value: + name: "QoS Policy Network" + description: "Request defines a Trust Domain with QoS policies." + enabled: true + accessDetails: + - <<: *wifi-wpa3-personal-example + policies: + <<: *max-bandwidth-policy-example + serviceId: *service-uuid-example + + ## Example responses + TrustDomainResponseBasic: + summary: Basic Trust Domain Response + description: Example of a created Trust Domain with minimal details. + value: + id: *uuid-example + name: "Basic Trust Domain" + description: "A basic trust domain example" + enabled: true + accessDetails: + - <<: *wifi-wpa2-personal-example + serviceId: *service-uuid-example + createdAt: "2025-10-21T14:27:08.312Z" + createdBy: *created-by-example + modifiedAt: "2025-10-21T14:27:08.312Z" + modifiedBy: *modified-by-example + + TrustDomainResponseWiFiThread: + summary: Created Trust Domain (Wi-Fi + Thread) + description: Example of a created Trust Domain including Wi-Fi and Thread access details and populated policies. + value: + id: *uuid-example + name: "Primary WiFi Network" + description: "Primary home Wi-Fi Network for all devices" + enabled: true + expiration: "2025-10-21T14:27:08.312Z" + policies: + <<: *egress-allowed-list-policy-example + accessDetails: + - <<: *wifi-wpa3-personal-example + - <<: *thread-structured-example + serviceId: *service-uuid-example + createdAt: "2025-10-21T14:27:08.312Z" + createdBy: *created-by-example + modifiedAt: "2025-10-21T14:27:08.312Z" + modifiedBy: *modified-by-example-2 diff --git a/original/NetworkAccessManagement/code/API_definitions/network-access-management.yaml b/original/NetworkAccessManagement/code/API_definitions/network-access-management.yaml new file mode 100644 index 0000000000000000000000000000000000000000..25af8ef7083edb87bc0e330d3116b99a58989946 --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/network-access-management.yaml @@ -0,0 +1,738 @@ +openapi: 3.0.3 + +info: + title: Home Devices - Network Access Management + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + description: | + Service enabling API for managing network operator supplied network access devices. This API's initial focus is on + managing **Trust Domains** and device reboot requests. + + # Introduction + A Trust Domain is a network access configuration where each configuration is for a logically separated Local + Area Network (LAN). API consumers can create, modify, or remove these networks which could be useful in + scenarios such as: + + - A property owner wants to create a temporary network for the duration of a short-term booking or long-term rental. + - A property manager wants to replicate the network access details across multiple network access devices at one or + more locations such as common areas, offices, etc. + - A security/privacy-minded user wants to create one or more networks for their guests or Internet-of-Thing (IoT) + network clients. + + A reboot request is simply a request to reboot a network operator supplied network access device. API consumers + can create these requests which could be useful in scenarios such as: + + - A property owner wants to recover from a faulty network state by rebooting a gateway device. + - A property manager wants to reboot multiple devices at one or more locations such as common areas, offices, etc. + + # Relevant Terms and Definitions + - **Trust Domain**: a declarative, intent-level grouping that defines which devices are permitted to communicate with each other as if they were on the same LAN and what high-level access policies apply to that group. + - **Reboot Request**: A request to reboot a network operator supplied network access device. + - **Network Access Device**: A network operator supplied network access device that supports network segmentation technologies. Multiple devices + that support LAN connectivity across the same Trust Domain (e.g., mesh Wi-Fi, Thread personal area network, + etc.) SHOULD be presented as a single device for implementations of this API. + - **API Provider**: Provider that implements this API. + - **Network Operator**: Service provider that has operational control of supporting devices. + - **Service Owner**: Customer of a network operator and resource owner with one or more devices that supports this + API across one or more service sites. + - **Service Site**: A distinct service owner location, as interpreted by the network operator, with one or more + devices. A service site typically has a one-to-one relationship with the mailing address of the location. Network + operators that support a single identity or interchangeable identities for multiple service sites at the same + mailing address (e.g., a residential and business account, an office and common area account, etc.) MUST provide + some distinction in the property address (e.g., attn: Home Office, attn: Common Area, etc.). Multiple service + sites, for the same mailing address, but for unrelated service owner identities, do not have this requirement. + - **End-User**: The user connecting to a Trust Domain with a network client. + - **Network Client**: End-user equipment connecting to a Trust Domain (e.g., laptop, phone, IoT device, etc.). + - **API Consumer**: A first- or third-party software system using this API. + + # API Functionality + This API allows API Consumers to manage Trust Domains and reboot network access devices. + + ### Authorization and authentication + + The "CAMARA Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + ### Scopes + Scopes are used to protect the service owner's information and privacy. The general format is + `--`. A resource may be further broken down into `-` or + `-` for granular permissions. Scopes also control output information as opposed to just + authorizing endpoints. Each endpoint definition will clearly state what scopes are needed for access and which are + needed to access additional information. Below are some general rules for scopes in this API. + + - Regulated information, such as physical locations or hardware addresses of network devices, have special scopes. + Network operators are expected to follow any local regulations when sharing this information with an API client. + - Scopes have inheritance when one scope would otherwise require the inherited scope. + - Read scopes for one resource impacts the output of another resource when the requested resource has a relationship + with the first (e.g., listing networks on a device requires both device and network read scopes). + + | Scope | Description | + |-------|-------------| + | **network-access-management:trust-domains** | Manage the caller's own Trust Domains (create, modify, delete, view). | + | **network-access-management:trust-domains:read-all** | Read all Trust Domains belonging to the subscriber, including those created by other clients (requires subscriber consent). | + | **network-access-management:reboot** | Create, list, and manage Reboot Requests for owned devices. | + | **network-access-management:services:read** | List services accessible to the authenticated identity | + + ## General Usage + This API is intended for creating, modifying, or deleting Trust Domains using the `/trust-domains` endpoints + to build access detail configurations. The `/service-sites` endpoints are used for iterating over a service owner's + locations. The exact location may be requested with an additional scope to assist with reconciling information about + service sites when the API client operator has an existing relationship with the service owner. Similarly, the + `/devices` endpoints are used for iterating over and configuring a service owner's devices. The hardware address + may be requested for the same purpose of reconciling information from another source (e.g., database, persons with + physical device access, etc.). + + ## Comments for API Clients + + ### Reboot Requests + Reboot Requests provide a declarative mechanism for API clients to trigger an + immediate or scheduled reboot of one or more Network Access Devices associated + with a subscriber. The following clarifies expected behavior, device inference + rules, and recommended client patterns. + + #### Device Targeting + Clients MAY target devices in one of two ways: + + 1. **Explicit Targeting** + The client provides a `devices` array containing one or more device UUIDs. + This mode MUST be used when: + - multiple devices exist for the subscriber + - reboot is intended for a subset of devices + - the provider indicates that inference is unsupported + + 2. **Implicit (“Default Device”) Targeting** + Clients MAY omit the `devices` array to reboot a default device, if and only if: + - exactly one device is provisioned for the subscriber + - the provider supports inference + - the device is reboot-capable + + If inference fails, the request MUST be rejected (e.g., 400 INVALID_ARGUMENT or + 422 MISSING_IDENTIFIER). + + #### Behavior Guarantees + + - If `devices` is omitted and inference succeeds, the response MUST contain the + provider-resolved device list. + - Validation is atomic: if any device ID is invalid, unauthorized, or not + reboot-capable, the request MUST fail without side effects. + - Partial success is not allowed. + - Providers MAY reject duplicate reboot requests targeting the same devices and time. + + #### Interaction with Related Endpoints + + - `GET /network-access-devices` + Used to enumerate devices and their configuration. + + - `POST /reboot-requests` + Create a reboot request (immediate or scheduled). + + - `GET /reboot-requests/{id}` + Retrieve the status of a previously-created request. Implementations MAY extend + the status model over time. + + #### Recommended Client Flow + + 1. (Optional) Query device capabilities using `/network-access-devices`. + 2. If multiple devices exist or inference is unsupported, build an explicit + device list. + 3. Create the reboot request with immediate or scheduled execution (`atTime`). + 4. (Optional) Poll the individual reboot request status for asynchronous flows. + + ## Comments for Network Operators + The following comments are for Network Operators implementing this API. + + ### Auto-Deleting Trust Domains + When a Trust Domain is not configured on any device the network configuration and its identifier SHOULD be + auto-deleted. API clients MUST not be expected to delete Trust Domains not configured on any device. + + ### Mesh Systems + Mesh systems SHOULD be represented as a single device when implementing this API due to the undefined behavior of + LAN connectivity across multiple devices with the same Trust Domain. The recommendation is to use the gateway + hardware address of the mesh system when exposing that field, though the hardware address of any node in the mesh + may be used. If an end-user replaces the equipment, all existing Trust Domains SHOULD be synced to the new + device representing this mesh. Alternatively, a synthetic hardware address may also be used if the specification + for the address type allows. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/NetworkAccessManagement + +servers: + - url: "{apiRoot}/network-access-management/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Services + description: Operations to list network services accessible to the authenticated identity + - name: Trust Domains + description: Operations to Create and Manage Trust Domains + - name: Reboot Requests + description: | + Operations to Create and Manage Reboot Requests for Network Access Devices + +paths: + + /services: + get: + tags: + - Services + summary: Get all services accessible to the authenticated identity + security: + - openId: + - network-access-management:services:read + operationId: getServices + description: | + Returns all services accessible to the calling identity. Services represent + a logical commercial relationship between a subscriber and a network operator, + typically corresponding to a unique service account or subscription. + + This endpoint supports workflows where an API Consumer (e.g., AirBnB, Amazon) + has received subscriber authorization and must enumerate services to link with + Network Client Devices or Trust Domains. + + responses: + "200": + description: Contains all services associated with the identity + content: + application/json: + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/ServiceList" + "401": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic401" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + + + /services/{serviceId}: + get: + tags: + - Services + summary: Get a service by ID + security: + - openId: + - network-access-management:services:read + operationId: getService + description: | + Returns a specific service corresponding to the given `serviceId`. + + This can be used to inspect service metadata prior to using it in other + API operations such as Trust Domain creation. + + **Required Scopes:** + - `network-access-management:services:read` + + parameters: + - name: serviceId + in: path + required: true + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/ServiceId" + description: | + The ID of the service to retrieve. + + Must be a valid UUID as defined by RFC 4122 (versions 1-5) using only lowercase hexadecimal characters. + responses: + "200": + description: Information about the service + content: + application/json: + schema: + $ref: "modules/Services/Services.yaml#/components/schemas/Service" + "401": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic401" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + + /trust-domains/capabilities: + get: + tags: + - Trust Domains + summary: Get Trust Domain capabilities + security: + - openId: + - network-access-management:trust-domains + operationId: getTrustDomainCapabilities + description: | + Retrieves the set of Trust Domain configuration capabilities supported by the API provider. + Capabilities describe supported access types, policy constraints, and configuration limits. + + This endpoint enables API clients to discover: + - Which access types are supported (Wi-Fi variants, Thread modes, etc.) + - What policy types are available + - Operational limits and constraints + - Advanced features and configuration options + + Use this endpoint before creating Trust Domains to ensure your configuration + is supported by the target API provider/network operator. + + responses: + "200": + description: Trust Domain capabilities supported by this API provider + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomainCapabilities.yaml#/components/schemas/TrustDomainCapabilities" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /trust-domains: + post: + tags: + - Trust Domains + summary: Create a new Trust Domain + security: + - openId: + - network-access-management:trust-domains + description: | + Creates and returns the new Trust Domain. + + operationId: createTrustDomain + requestBody: + description: Details of the Trust Domain to be created + required: true + content: + application/json: + schema: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomainCreate' + examples: + TrustDomainCreateWpa2Personal: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateWpa2Personal' + TrustDomainCreateInferredSsid: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateInferredSsid' + TrustDomainCreateThreadStructured: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateThreadStructured' + TrustDomainCreateEphemeral: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateEphemeral' + TrustDomainCreateQoSPolicies: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainCreateQoSPolicies' + responses: + '201': + description: Trust Domain created successfully + content: + application/json: + schema: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain' + examples: + TrustDomainResponseBasic: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseBasic' + TrustDomainResponseWiFiThread: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseWiFiThread' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + get: + tags: + - Trust Domains + summary: Retrieves all Trust Domains visible to the calling API client + security: + - openId: + - network-access-management:trust-domains + - openId: + - network-access-management:trust-domains:read-all + operationId: getTrustDomains + description: | + Retrieves all Trust Domains visible to the calling API client. + + If the caller has `network-access-management:trust-domains`, the response is limited to + Trust Domains created by the caller. If the caller has `network-access-management:trust-domains:read-all`, + the response includes all Trust Domains associated with the subscriber. + responses: + + "200": + description: Contains information about all trust domains + content: + application/json: + schema: + type: array + items: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /trust-domains/{trustDomainId}: + parameters: + - $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/parameters/trustDomainId' + + get: + tags: + - Trust Domains + summary: Get a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + - openId: + - network-access-management:trust-domains:read-all + operationId: getTrustDomain + description: | + Retrieves the Trust Domain identified by the given ID. Visibility of this Trust Domain depends on the caller's scope and ownership: + - `trust-domains` restricts access to caller-owned Trust Domains. + - `trust-domains:read-all` allows retrieval of any Trust Domain associated with the subscriber. + + responses: + + "200": + description: Contains information about the specified trust domain + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + examples: + TrustDomainResponseBasic: + $ref: 'modules/TrustDomains/TrustDomains.yaml#/components/examples/TrustDomainResponseBasic' + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + patch: + tags: + - Trust Domains + summary: Update a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + operationId: updateTrustDomain + description: | + Updates the Trust Domain identified by the given ID. Any changes are automatically applied to all network access devices where the Trust Domain is configured. + + requestBody: + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomainUpdate" + required: true + responses: + "200": + description: Contains information about the updated trust domain + content: + application/json: + schema: + $ref: "modules/TrustDomains/TrustDomains.yaml#/components/schemas/TrustDomain" + + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + delete: + tags: + - Trust Domains + summary: Delete a specific Trust Domain + security: + - openId: + - network-access-management:trust-domains + operationId: deleteTrustDomain + description: | + Deletes the Trust Domain identified by the given ID and removes its configuration from all network access devices where it is applied. + + responses: + "204": + description: Trust Domain deleted successfully + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /network-access-devices: + get: + tags: + - Reboot Requests + summary: Get all Network Access Devices associated with the service owner + security: + - openId: + - network-access-management:reboot + operationId: getNetworkAccessDevices + description: | + Retrieves all Network Access Devices associated with the subscriber that the caller is authorized to manage using the `network-access-management:reboot` scope. + responses: + "200": + description: Contains the list of network access devices + content: + application/json: + schema: + $ref: "modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/schemas/NetworkAccessDeviceList" + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /network-access-devices/{networkAccessDeviceId}: + get: + tags: + - Reboot Requests + summary: Get a specific Network Access Device + security: + - openId: + - network-access-management:reboot + operationId: getNetworkAccessDevice + description: | + Retrieves the Network Access Device that matches the given ID. + parameters: + - $ref: 'modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/parameters/networkAccessDeviceId' + responses: + "200": + description: Contains information about the specified network access device + content: + application/json: + schema: + $ref: "modules/NetworkAccessDevices/NetworkAccessDevices.yaml#/components/schemas/NetworkAccessDevice" + "400": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic400" + "403": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic403" + "404": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic404" + "500": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic500" + "503": + $ref: "common/CAMARA_common.yaml#/components/responses/Generic503" + + /reboot-requests: + post: + tags: + - Reboot Requests + summary: Create a new Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Creates a new Reboot Request targeting one or more Network Access Devices. + operationId: createRebootRequest + requestBody: + description: | + Creates a reboot request for one or more network access devices. Supports two targeting modes: + + Targeting modes: + - Inferred (implicit/default device): Omit the 'devices' array to request a reboot of the single + default device associated with the subscriber context. This is only valid when exactly one + device is eligible. If no default device exists or multiple devices are provisioned, the + request MUST be rejected (e.g. 400 INVALID_ARGUMENT or 422 MISSING_IDENTIFIER). + - Explicit (targeted devices): Provide a 'devices' array of one or more device UUIDs to request + reboots on those specific devices. Validation MUST fail if any supplied device ID is unknown, + not reboot-capable, or the caller lacks authorization. + + Scheduling: + - Immediate reboot: Omit 'atTime'. + - Scheduled reboot: Include 'atTime' (RFC 3339 with timezone). Time MUST be in the future; past + values SHOULD produce a 400 OUT_OF_RANGE error. + + Idempotency / duplication: + - Multiple identical pending reboot requests (same device set and same atTime) MAY be rejected + with 409 CONFLICT or collapsed by implementation. + + Error conditions (examples): + - 400 INVALID_ARGUMENT: Unsupported time format, too many device IDs, malformed UUID. + - 404 IDENTIFIER_NOT_FOUND: One or more device IDs not found. + - 403 PERMISSION_DENIED: Caller lacks scope or device ownership. + - 409 CONFLICT: Reboot already scheduled for the same devices and time. + - 422 MISSING_IDENTIFIER (implementation-specific): 'devices' omitted but no default device. + + Behavioral guarantees: + - If 'devices' omitted and inference succeeds, the response MUST reflect the resolved device list. + - If any device fails validation, no reboot request is created (atomic failure). + - Partial success is NOT permitted. + required: true + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequestCreate' + examples: + RebootRequestCreateImmediate: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/examples/RebootRequestCreateImmediateDefaultDevice' + RebootRequestCreateScheduled: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/examples/RebootRequestCreateScheduledMultipleDevices' + responses: + '201': + description: Reboot Request created successfully + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '422': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic422' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + get: + tags: + - Reboot Requests + summary: Get all Reboot Requests created by the calling API client + security: + - openId: + - network-access-management:reboot + operationId: getRebootRequests + description: | + This endpoint returns a list of Reboot Requests associated with the service owner created by the calling API client. + responses: + '200': + description: Contains information about all reboot requests + content: + application/json: + schema: + type: array + items: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + /reboot-requests/{rebootRequestId}: + parameters: + - $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/parameters/rebootRequestId' + + get: + tags: + - Reboot Requests + summary: Get a specific Reboot Request + security: + - openId: + - network-access-management:reboot + operationId: getRebootRequest + description: | + Retrieves the Reboot Request that matches the given ID. + responses: + '200': + description: Contains information about the specified Reboot Request + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + patch: + tags: + - Reboot Requests + summary: Update an existing Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Updates an existing Reboot Request to modify its scheduled time or cancel it. + operationId: updateRebootRequest + requestBody: + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequestUpdate' + required: true + responses: + '200': + description: Reboot Request updated successfully + content: + application/json: + schema: + $ref: 'modules/RebootRequests/RebootRequests.yaml#/components/schemas/RebootRequest' + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '409': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic409' + '422': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic422' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + + delete: + tags: + - Reboot Requests + summary: Delete an existing Reboot Request + security: + - openId: + - network-access-management:reboot + description: | + Deletes an existing Reboot Request, cancelling the scheduled reboot if it has not yet occurred. + operationId: deleteRebootRequest + responses: + '204': + description: Reboot Request deleted successfully + '400': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic400' + '403': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic403' + '404': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic404' + '500': + $ref: 'common/CAMARA_common.yaml#/components/responses/Generic500' + +components: + securitySchemes: + openId: + $ref: 'modules/NAM_Common.yaml#/components/securitySchemes/openId' diff --git a/original/NetworkAccessManagement/code/API_definitions/redocly.yaml b/original/NetworkAccessManagement/code/API_definitions/redocly.yaml new file mode 100644 index 0000000000000000000000000000000000000000..12aae9a283523f7887b6a7ec0de32f27ab18baa2 --- /dev/null +++ b/original/NetworkAccessManagement/code/API_definitions/redocly.yaml @@ -0,0 +1,10 @@ +extends: + - recommended + +rules: + no-unused-components: "off" + no-empty-servers: "off" + +resolve: + file: + allowedFileExtensions: [".yaml", ".yml"] diff --git a/original/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story.md b/original/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..c0498e538a98eea616d6b1abe3757db50f7655be --- /dev/null +++ b/original/NetworkAccessManagement/documentation/API_documentation/DeviceRebootRequest_User_Story.md @@ -0,0 +1,9 @@ +| **Item** | **Details** | +|------------------------------|-------------| +| **Summary** | As a service owner or property manager, I want to issue reboot requests for my API Provider-managed network access devices (such as gateways or mesh controllers) to recover from faulty network states or to perform administrative resets, ensuring reliable connectivity for tenants or guests. | +| **Roles, Actors and Scope** | **Roles:** customer:user
                                                    **Actors:** Service owners, property managers, API providers.
                                                    **Scope:** Trouble to Resolution (T2R) - Issue immediate or scheduled reboot requests for specific devices. Retrieve status of previously created reboot requests. | +| **Pre-conditions** | 1. The API consumer is onboarded and holds credentials with proper scopes (e.g., `reboot-requests:write`, optionally `devices:write`).
                                                    2. The devices are installed and managed by the API provider supporting reboot management. | +| **Begins when** | The API client makes a `POST` request to `/reboot-requests` with a list of device IDs and an optional `atTime` to schedule the reboot. | +| **Ends when** | The reboot is executed by the API Provider-managed device or the request is withdrawn. | +| **Post-conditions** | - The specified device(s) reboot, recovering connectivity or clearing transient faults.
                                                    - System logs are updated to reflect administrative action. | +| **Exceptions** | - `400 Bad Request`: Malformed request body (e.g., invalid time format).
                                                    - `401 Unauthorized`: Access token issues.
                                                    - `403 Forbidden`: Lack of permission for target devices.
                                                    - `404 Not Found`: Specified reboot request or device ID does not exist.| \ No newline at end of file diff --git a/original/NetworkAccessManagement/documentation/API_documentation/README.MD b/original/NetworkAccessManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..a393d912719c730e594f9220ac1f51acf13c01d9 --- /dev/null +++ b/original/NetworkAccessManagement/documentation/API_documentation/README.MD @@ -0,0 +1,57 @@ +# CAMARA User Story Guidance + +This document summarizes how to create or modify CAMARA-aligned User Stories using the **Commonalities User Story Template** and how to determine the correct **Scope** value based on the **TM Forum NaaS (TMF 909A)** lifecycle definitions. + +--- + +## 1. Authoritative Sources + +Any information in this guide is derived from the following authoritative sources: + +| Source | Description | Link | +|--------|--------------|------| +| **CAMARA Commonalities – User Story Template** | Canonical template defining fields, structure, and allowed values (Roles, Scope, etc.). | [github.com/camaraproject/Commonalities/documentation/Userstory-template.md](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) | +| **CAMARA Commonalities – Guidelines** | Explains how Commonalities artifacts (User Stories, API Guidelines, etc.) are structured. | [camaraproject.org/commonalities](https://camaraproject.org/commonalities/) | +| **TM Forum TMF 909A – NaaS API Component Suite Profile v1.5** | Defines the lifecycle areas used for the “Scope” field. | [TM Forum TMF 909A – NaaS API Component Suite Profile](https://engage.tmforum.org/HigherLogic/System/DownloadDocumentFile.ashx?DocumentFileKey=70781cfc-1ebb-4ef9-b728-44b34e9c14a1) | +| **TM Forum Open APIs** | APIs referenced for each lifecycle area (TMF 633, 640, 645, 653, 656, 677). | [tmforum.org/open-apis](https://www.tmforum.org/open-apis/) | + +Start with the [CAMARA Commonalities – User Story Template](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md) for a comprehensive understanding of user story structure and requirements. From there, you will note a `ReferenceArchitecture` powerpoint is mentioned; this includes slides that summarize the alignment with TM Forum lifecycles, which is further detailed in Section 3 of this document. + +--- + +## 2. User Story Template Overview + +Each CAMARA User Story should include: + +| Field | Description | Guidance | +|-------|--------------|-----------| +| **Title / Summary** | “As a \, I want \ so that \.” | User-centric phrasing. | +| **Roles** | Acceptable values: `customer:user`, `customer:administrator`, `customer:business manager` (from Commonalities template). | Choose based on the actor’s function and access level. | +| **Actor(s)** | Entity or system executing or triggering the story (e.g., API Consumer, API Provider, Service Owner). | Prefer roles over specific implementations. | +| **Scope** | Lifecycle area(s) impacted. See Section 3 below. | Select **one or more** of: Design time, P2O, O2A, U2C, T2R. | +| **Pre-conditions / Begins when** | Required system or business state before the story starts. | Often references catalog or active service. | +| **Steps** | Numbered flow of actions. | Keep technology-neutral. | +| **Post-conditions / Ends when** | Expected outcome or state. | Clarify data, service, or operational result. | +| **Exceptions** | Deviations or failure modes. | Include both business and technical exceptions if relevant. | + +--- + +## 3. Scope Reference (Lifecycle Areas) + +The **Scope** field classifies a user story according to the TM Forum NaaS (TMF 909A) lifecycle model. +Use this section to determine where a story fits. + +| Scope | TM Forum Reference | Summary | Typical APIs / Activities | +|--------|--------------------|----------|----------------------------| +| **Design Time** | TMF 909A § 2.1.5 (Service Catalog) | “Concept-to-Market” activities defining new service specifications. Used for retrieving, creating, or updating service specs prior to runtime. | TMF 633 Service Catalog Management | +| **Prospect to Order (P2O)** | TMF 909A § 2.1.2 | Evaluate what products or services can be offered to a customer. Includes availability checks, feasibility analysis, and resource reservation. | TMF 645 Service Qualification | +| **Order to Activate (O2A)** | TMF 909A § 2.1.1 | Fulfil and activate ordered services, including in-flight modification, suspension, or removal. Covers the operational lifecycle of a service instance. | TMF 640 Activation & Configuration | +| **Usage to Cash (U2C)** | TMF 909A § 2.1.4 | Measure and report service usage for billing or quota management. Includes retrieval, periodic reporting, and threshold notifications. | TMF 677 Usage Consumption | +| **Trouble to Resolution (T2R)** | TMF 909A § 2.1.3 | Monitor, diagnose, and restore services when faults occur. Includes testing, problem creation, updates, and closure. | TMF 656 Service Problem Mgmt, TMF 653 Service Test | + +> **Tip:** +> - If the story involves designing or publishing a service → **Design Time** +> - If it checks availability or feasibility before order → **P2O** +> - If it provisions or modifies active services → **O2A** +> - If it deals with usage or quotas → **U2C** +> - If it handles incidents or assurance → **T2R** diff --git a/original/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story.md b/original/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..8a6b053f1f5cb81fee0f44cd90c559d2b0b1a24d --- /dev/null +++ b/original/NetworkAccessManagement/documentation/API_documentation/TrustDomainsUser_Story.md @@ -0,0 +1,10 @@ +| **Item** | **Details** | +|-----------|-------------| +| **Summary** | As a **service owner or API Consumer**, I want to create, modify, and delete **logically isolated network configurations** (Trust Domains) on **API Provider-managed network access devices** (such as gateways or mesh Wi-Fi), defining both network access details and associated policies (such as device limits, bandwidth, or egress rules), so that I can securely segment and govern connectivity for tenants, guests, or IoT devices with predictable behavior and lifecycle control. | +| **Roles, Actors, and Scope** | **Roles:** `customer:user`.
                                                    **Actors:** Service owners, API Consumers, IoT integrators, API providers.
                                                    **Scope:** **Order to Activate (O2A)** — Covers provisioning, modification, and removal of active network configurations. Trust Domain management corresponds to TM Forum **TMF 909A § 2.1.1 “Order to Activate”**, which governs service activation and configuration actions. | +| **Pre-conditions** | 1. The API Consumer has been onboarded with the API provider and obtained valid access credentials with appropriate scopes (e.g., `network-access-management:trust-domains:write`).
                                                    2. The service owner has one or more registered API-provider-managed devices at their premises.
                                                    3. The API provider has implemented the **Network Access Management (NAM)** API supporting Trust Domain configuration. | +| **Begins when** | The API Consumer sends a `POST` request to `/trust-domains` to create a new Trust Domain (optionally including expiration), providing Wi-Fi access details such as SSID, security mode, and credentials, or to `PATCH`/`DELETE` for modification or removal. | +| **Ends when** | The requested Trust Domain is created, updated, or deleted, and the configuration change is successfully reflected on the associated network access devices. | +| **Post-conditions** | - New Trust Domains are provisioned and active on designated or inferred network devices, enforcing logical traffic segmentation.
                                                    - Updated configurations replace previous credentials or policies.
                                                    - Trust Domains that are no longer assigned to any device are automatically removed. | +| **Exceptions** | - **400 Bad Request:** Invalid request parameters (e.g., malformed SSID, unsupported security mode).
                                                    - **401 Unauthorized:** Missing, invalid, or expired access token.
                                                    - **403 Forbidden:** Caller lacks sufficient authorization scope or role.
                                                    - **404 Not Found:** Referenced device or Trust Domain ID does not exist.
                                                    - **409 Conflict:** Attempt to delete a non-removable or in-use Trust Domain. | +| **References** | - [CAMARA Commonalities – User Story Template](https://github.com/camaraproject/Commonalities/blob/main/documentation/Userstory-template.md)
                                                    - [TM Forum TMF 909A v1.5 § 2.1.1 – Order to Activate](https://projects.tmforum.org/wiki/display/API/TMF640+Activation+and+Configuration+API+REST+Specification)| diff --git a/original/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist.md b/original/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..25296053563f7fc13a5aa66ada343cb1da5eca61 --- /dev/null +++ b/original/NetworkAccessManagement/documentation/API_documentation/network-access-management-API-Readiness-Checklist.md @@ -0,0 +1,30 @@ +# API Readiness Checklist + +Checklist for network-access-management 0.1.0-alpha.1 in r1.1. + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:---------------:| +| 1 | API definition | M | M | M | M | Y | [relative link](../../code/API_definitions/network-access-management.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.4 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in yaml | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | N | | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | N | | +| 11 | Change log updated | M | M | M | M | N | [relative link](../../CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | N | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166949/NetworkAccessManagement+API+description) | + +To fill the checklist: + +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/NetworkAccessManagement/documentation/SupportingDocuments/README.MD b/original/NetworkAccessManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/NetworkAccessManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/NetworkInsights/README.md b/original/NetworkInsights/README.md new file mode 100644 index 0000000000000000000000000000000000000000..560ae2254ae970206ec46ebbd99af18284cb1e36 --- /dev/null +++ b/original/NetworkInsights/README.md @@ -0,0 +1,44 @@ + + + + + + + + + +# NetworkInsights + +Sandbox API Repository to describe, develop, document, and test the NetworkInsights Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/fQCoBg) + +## Scope + +* Service API(s) “NetworkInsights” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. By providing a holistic view — from infrastructure health to user traffic trends — this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. +* Describe, develop, document, and test the API(s) +* Started: May 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/fQCoBg) !! update this link to your minutes archive page using the "Share" link and delete the task + +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/NetworkInsights/code/API_definitions/network-health-assessment.yaml b/original/NetworkInsights/code/API_definitions/network-health-assessment.yaml new file mode 100644 index 0000000000000000000000000000000000000000..2334f805c8c2e2995fec0e7bfeafd73d17237508 --- /dev/null +++ b/original/NetworkInsights/code/API_definitions/network-health-assessment.yaml @@ -0,0 +1,348 @@ +openapi: 3.0.3 +info: + title: Network Health Assessment + description: | + Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. + It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. + By providing a holistic view — from infrastructure health to user traffic trends — this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. + + # Introduction + This API allows users to query the health score of a specified network, which consists of multiple components including the wireless network, transmission network, and core network. + By calculating the health score for each component and then applying weighted calculations, the API provides a comprehensive health score result for the specified network. + + The health score is a value evaluated by the platform based on the performance/fault indicator status of a specific network module, ranging from 0 to 100. Scores above 90 are considered excellent/healthy, + scores between 60 and 80 indicate varying degrees of issues, and scores below 60 mean the network is basically unable to provide normal services. + A specified network contains different network modules, such as wireless networks, transport networks, and core networks. + The “netType” parameter can be used to query the health assessment of the corresponding network module or the entire network. + The health assessment mechanism periodically evaluates the performance and alarm data of network devices and generates reports. + This API provides the latest report results by default. + + # API functionality + The API provides the following functionality: + - Query the health scores of different network modules in the specified network at the latest point in time. + + # Request Parameters Definition: + * **networkId**: Unique identifier of the Assessment network (UUID format). + * **netType**: Modules within the network. Optional values are: NET (the entire network), NET_WIRELESS (wireless network), NET_TRANSPORT (transport network), NET_CORE (core network). + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkInsights +servers: + - url: "{apiRoot}/network-health-assessment/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Health Assessment + description: Query Network Health Assessment scores for specific network modules. +paths: + /health-scores: + post: + tags: + - Network Health Assessment + summary: Query the latest network health score + description: | + Query the health assessment results of the specified network module at the latest time point. + - Returns the health score (0-100) for the selected network module. + operationId: getHealthScores + security: + - openId: + - network-health-assessment:health-scores:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + type: object + required: + - networkId + - netType + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + netType: + $ref: "#/components/schemas/NetTypeEnum" + examples: + EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + responses: + "200": + description: Health score queried successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/HealthInfo" + examples: + RESPONSE_NET: + $ref: "#/components/examples/RESPONSE_EXAMPLE_NET" + RESPONSE_NET_WIRELESS: + $ref: "#/components/examples/RESPONSE_EXAMPLE_NET_WIRELESS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Correlator string, UUID format recommended but any string matching the pattern can be used + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + maxLength: 256 + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network ID in UUID format (unique identifier of the analyzed network) + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + Score: + title: HealthScore + description: Value of the health score (0-100, higher is better) + type: number + format: double + minimum: 0 + maximum: 100 + example: 94.56 + + HealthInfo: + title: NetworkHealthInfo + description: Network health score information + allOf: + - type: object + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + netType: + $ref: "#/components/schemas/NetTypeEnum" + score: + $ref: "#/components/schemas/Score" + scoringTime: + type: string + format: date-time + maxLength: 64 + description: Latest time point of the health score calculation. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2025-12-01T12:00:00Z" + required: + - networkId + - netType + - score + - scoringTime + + NetTypeEnum: + title: NetworkModuleType + description: Enums of network module types + type: string + enum: + - NET + - NET_WIRELESS + - NET_TRANSPORT + - NET_CORE + example: "NET" + + ErrorInfo: + type: object + description: A structured error response providing details about a failed request, including the HTTP status code, an error code, and a human-readable message + required: + - status + - code + - message + properties: + status: + type: integer + format: int32 + minimum: 100 + maximum: 599 + description: HTTP response status code + code: + type: string + maxLength: 96 + description: A human-readable code to describe the error + message: + type: string + maxLength: 512 + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + examples: + EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + RESPONSE_EXAMPLE_NET: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET" + score: 94.56 + scoringTime: "2025-12-01T12:00:00Z" + RESPONSE_EXAMPLE_NET_WIRELESS: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + netType: "NET_WIRELESS" + score: 90.12 + scoringTime: "2025-12-01T12:00:00Z" diff --git a/original/NetworkInsights/code/API_definitions/network-traffic-analysis.yaml b/original/NetworkInsights/code/API_definitions/network-traffic-analysis.yaml new file mode 100644 index 0000000000000000000000000000000000000000..9433ebbc023c7136aa27198ea2eb6627541c63fe --- /dev/null +++ b/original/NetworkInsights/code/API_definitions/network-traffic-analysis.yaml @@ -0,0 +1,403 @@ +openapi: 3.0.3 +info: + title: Network Traffic Analysis + description: | + Network Insight offers a unified analytical platform for specific networks, such as private networks and slices, focusing exclusively on aggregated network-level data rather than individual device information. + It empowers users to both evaluate the overall network health through a comprehensive, component-based scoring system and to analyze service traffic patterns with customizable granularity. + By providing a holistic view-from infrastructure health to user traffic trends-this API suite delivers the critical, real-time data needed for comprehensive network monitoring, strategic performance optimization, and effective early warning systems. + + # Introduction + The Network Traffic Analysis API utilizes DPI collection technology to capture communication traffic between all services or terminals within the network. + By correlating service-specific data with devices and port resources, it aggregates and calculates the traffic flow for each service, thereby deriving service-based traffic distribution across the entire network. + This data helps identify high-traffic services and traffic load conditions during different time periods, facilitating the provision of appropriate bandwidth for critical services through slicing technology, ultimately enabling efficient utilization of network resources. + + # API functionality + The API provides the following functionality: + - It allows users to directly query access traffic statistics for all services within a specified time period, including the number of accesses and the cumulative values of uplink and downlink traffic. + + # Request Parameters Definition: + * **networkId**: Unique identifier of the analyzed network (UUID format). + * **timePeriod**: Time range for network analysis (start + end time, RFC 3339 with timezone). + * **frequency**: Analysis granularity (enumeration: 'DAY', 'HOUR'). + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkInsights +servers: + - url: "{apiRoot}/network-traffic-analysis/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Traffic Analysis + description: The API allows API consumers to query 5G traffic statistics information for aggregated network-level data. +paths: + /traffic-analysis: + post: + tags: + - Network Traffic Analysis + summary: Get network traffic analysis + description: | + Query 5G traffic statistics information for aggregated network-level data. + operationId: getTrafficAnalysis + security: + - openId: + - network-traffic-analysis:traffic-analysis:read + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + type: object + required: + - networkId + - timePeriod + - frequency + properties: + networkId: + $ref: "#/components/schemas/NetworkId" + timePeriod: + $ref: "#/components/schemas/TimePeriod" + frequency: + $ref: "#/components/schemas/Frequency" + examples: + ValidRequest: + value: + networkId: "123e4567-e89b-12d3-a456-426614174000" + timePeriod: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-07-01T12:00:00Z" + frequency: "DAY" + responses: + "200": + description: Successful response with network traffic analysis data + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficAnalysisResponse' + examples: + Success: + $ref: '#/components/examples/TrafficAnalysisSuccess' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Correlator string, UUID format recommended but any string matching the pattern can be used + type: string + pattern: '^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$' + maxLength: 256 + minLength: 1 + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + NetworkId: + description: Network ID in UUID format (unique identifier of the analyzed network) + type: string + format: uuid + example: "123e4567-e89b-12d3-a456-426614174000" + + TimePeriod: + type: object + description: Time range for network traffic analysis. A period of time defined by a start date and an end date + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-07-01T12:00:00Z" + required: + - startDate + + Frequency: + description: Analysis granularity (time interval for aggregation) + type: string + enum: ["DAY", "HOUR"] + example: "DAY" + + TrafficAnalysisResponse: + type: object + description: Response schema for traffic analysis + required: + - message + - data + properties: + message: + type: string + description: Human-readable status message + example: "Network traffic analysis has been completed" + maxLength: 256 + data: + type: object + description: Traffic analysis data + properties: + records: + type: array + description: Array of traffic records per application + minItems: 1 + maxItems: 1000 + items: + type: object + properties: + app: + type: string + description: Application name + example: "whatsapp" + maxLength: 128 + ipv4Address: + type: string + description: Application server IP ipv4 address + example: "202.112.17.122" + format: ipv4 + maxLength: 15 + description: + type: string + description: Application description + example: "A free cross-platform app for messaging, calls, and media sharing." + maxLength: 512 + accessCount: + type: integer + description: Total number of accesses to the application + minimum: 0 + example: 150 + accessUpFlow: + type: integer + description: Total upstream traffic (bytes) + minimum: 0 + example: 102400 # 100 KB + accessDownFlow: + type: integer + description: Total downstream traffic (bytes) + minimum: 0 + example: 204800 # 200 KB + accessFlow: + type: integer + description: Total traffic (up + down, bytes) + minimum: 0 + example: 307200 # 300 KB + startDate: + type: string + format: date-time + description: Start time of the record interval + example: "2024-06-07T00:00:00Z" + pattern: '^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}:\d{2}(Z|[+-]\d{2}:\d{2})$' + maxLength: 30 + endDate: + type: string + format: date-time + description: End time of the record interval + example: "2024-06-07T23:59:59Z" + pattern: '^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}:\d{2}(Z|[+-]\d{2}:\d{2})$' + maxLength: 30 + accessDate: + type: string + format: date + description: Date of the traffic record (YYYY-MM-DD) + example: "2024-06-07" + pattern: '^\d{4}-\d{2}-\d{2}$' + maxLength: 10 + total: + type: integer + description: Total number of application records + minimum: 0 + example: 22 + + ErrorInfo: + type: object + description: A structured error response providing details about a failed request, including the HTTP status code, an error code, and a human-readable message + required: + - status + - code + - message + properties: + status: + type: integer + format: int32 + description: HTTP response status code + code: + type: string + maxLength: 96 + description: A human-readable code to describe the error + message: + type: string + maxLength: 512 + description: A human-readable description of what the event represents + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + examples: + TrafficAnalysisSuccess: + value: + message: "Network traffic analysis has been completed" + data: + records: + - app: "whatsapp" + ipv4Address: "202.112.17.122" + description: "A free cross-platform app for messaging, calls, and media sharing." + accessCount: 150 + accessUpFlow: 102400 # 100 KB + accessDownFlow: 204800 # 200 KB + accessFlow: 307200 # 300 KB + startDate: "2024-06-07T00:00:00Z" + endDate: "2024-06-07T23:59:59Z" + accessDate: "2024-06-07" + total: 22 diff --git a/original/NetworkInsights/documentation/API_documentation/NHA_User_Story.md b/original/NetworkInsights/documentation/API_documentation/NHA_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..ce6a28c365368ba35530fc762f51dd1a56b2b105 --- /dev/null +++ b/original/NetworkInsights/documentation/API_documentation/NHA_User_Story.md @@ -0,0 +1,12 @@ +# Network Health Assessment (NHA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Insights API | +| API summary | **Overview**: For private network monitoring, general users cannot intuitively perceive network performance status or identify performance bottlenecks and faults from complex metrics. Therefore, it is necessary to analyze and integrate raw network and device performance data to achieve monitoring of the entire private network’s status from a higher level.
                                                    **Correlation with network-insight API**: The Network Insights API collects, analyzes, and visualizes network-related data, applying deep analysis and insights to enable private network users to understand what is happening on the network, identify potential issues, and make smarter decisions. Specifically, the Network Health Assessment API is based on a pre-configured service monitoring model (which allows for the selection of modules such as RAN, transport network, and core network, according to service conditions, and sets scoring rules, weights, and severe degradation thresholds for their key alarms and performance indicators to generate a health monitoring model). It performs comprehensive calculations to provide composite score data for each module and the entire private network, presenting private network users with an immediate and intuitive view of the business network status. Additionally, it allows for the retrieval of historical scores, prediction of future network performance trends, and the identification of network bottlenecks and fault location.
                                                    **Network Health Assignment API**: It allows users to directly query the latest health assessment score. Based on the health model, this may include scores for modules such as terminals, RAN, transport network, core network, and MEC, as well as a comprehensive score for all modules.

                                                    Proposed API Definitions
                                                    -Input Parameters:
                                                    structCode: module of Network (net, net_wireless, net_transnet, net_corer)

                                                    -Output Parameters:
                                                    time: The time of the score create.
                                                    valid: The validity of the score.
                                                    value: The score of the health.

                                                    An example: Health assessment relies on performance and alarm data from devices such as terminals, wireless base stations, and core network elements within the private network. The entire data management process can follow the steps below.
                                                    Resource Management: The computing platform needs to maintain information on all device assets within the private network and know which devices are included.
                                                    Performance and Alarm Collection: The computing platform can complete data collection via the device network management platform or by connecting directly to the devices.
                                                    Health Assessment Model Generation: Based on the nature of the private network service, indicators for terminals, base stations, or core network elements can be custom selected, and scoring rules can be set for these indicators.
                                                    Health Assessment Result Generation: Based on the collected data and the calculation model, health assessment score records are generated periodically.
                                                    Health Assessment Result Query: Private network users can query results for the most recent time point at any time.| +| Technical viability | This API requires the completion of device performance and alarm data collection. If collecting via a device management system, the collection protocol can be negotiated independently; if connecting directly to the device, collection via the SNMP protocol can be considered. Regarding the design of the health assessment calculation model, the key is to identify the indicators that best reflect performance and fault status across modules such as terminals, RAN, and core network. Then, based on the private network service type, set the weight and threshold for each indicator, and configure the source of the comparison value (period-over-period, year-over-year, or comparison against a fixed value).| +| Commercial viability | Health assessment is intended for organizations and individuals who need to monitor the status of their private network. It typically serves as a foundational feature for the monitoring dashboards of operators’ private network management platforms, and interfaces can also be opened up for private network users or third-party managed platforms to call for secondary development.| + +## ***Summary*** + +General private network users typically lack professional O&M capabilities and are unable to determine the actual operating status of the private network by directly inspecting devices or interpreting complex metric data provided by management platforms. Therefore, it is necessary to provide a series of higher-level visualization functions to facilitate self-management and self-operations for private network users.
                                                    The Network Health Assessment API provides such capabilities for monitoring personnel, enabling them to perform private network health self-checks based on a preconfigured health assessment calculation model. diff --git a/original/NetworkInsights/documentation/API_documentation/NTA_User_Story.md b/original/NetworkInsights/documentation/API_documentation/NTA_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..8099f7101b53a2a49d612a301c46853e37668222 --- /dev/null +++ b/original/NetworkInsights/documentation/API_documentation/NTA_User_Story.md @@ -0,0 +1,12 @@ +# Network Traffic Analysis (NTA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Insights API | +| API summary | **Overview**: For private network monitoring, general users cannot intuitively perceive network performance status or identify performance bottlenecks and faults from complex metrics. Therefore, it is necessary to analyze and integrate raw network and device performance data to achieve monitoring of the entire private network’s status from a higher level.
                                                    **Correlation with network-insight API**: The Network Insights API collects, analyzes, and visualizes network-related data, applying deep analysis and insights to enable private network users to understand what is happening on the network, identify potential issues, and make smarter decisions. Specifically, the Network Traffic Analysis API utilizes DPI collection technology to capture communication traffic between all services or terminals within the network. By correlating service-specific data with devices and port resources, it aggregates and calculates the traffic flow for each service, thereby deriving service-based traffic distribution across the entire network. This data helps identify high-traffic services and traffic load conditions during different time periods, facilitating the provision of appropriate bandwidth for critical services through slicing technology, ultimately enabling efficient utilization of network resources.
                                                    **Network Traffic Analysis API**: It allows users to directly query access traffic statistics for all services within a specified time period, including the number of accesses and the cumulative values of uplink and downlink traffic.

                                                    Proposed API Definitions
                                                    -Input Parameters:
                                                    startTime: Start time for the analysis in the format 'YYYY-MM-DD HH:mm:ss'.
                                                    endTime: End time for the analysis in the format 'YYYY-MM-DD HH:mm:ss'.
                                                    Domain ID (optional): The platform defines the unique identifier for the service..
                                                    period: Period for the analysis ('DAY', 'HOUR', etc.).
                                                    page: Page number for pagination (optional).
                                                    pageSize: Number of records per page for pagination (optional).

                                                    -Output Parameters:
                                                    app: Application name.
                                                    address: Application address.
                                                    description: Application description.
                                                    accessCount: Access count.
                                                    accessUpFlow: Upstream traffic flow.
                                                    accessDownFlow: Downstream traffic flow.
                                                    accessFlow: Total traffic flow.
                                                    startTime: Start time of the record.
                                                    endTime: End time of the record.
                                                    accessDate: Access date.

                                                    An example: Network traffic analysis relies on switches or UPFs to forward traffic data. The entire data management process can follow these steps:
                                                    Resource Management: The computing platform needs to maintain the private network service classification, as well as the relationship between services and application service addresses.
                                                    Data Collection: Utilizing DPI technology, all traffic data is intercepted via traffic tapping or mirrored ports and pushed to a dedicated data analysis server.
                                                    Data Statistical Analysis: Classify and organize data based on services.
                                                    Traffic Analysis Result Query: Private network users can query traffic analysis data for various services within a specified time period at any time.| +| Technical viability | This API requires the association of service addresses with service definitions. Additionally, it needs to intercept and calculate data for requests and responses accessing various service applications. Since the performance and stability of existing applications must not be impacted, traffic mirroring or optical splitting can be considered for data collection and analysis.| +| Commercial viability | Network traffic analysis is suitable only for organizations and individuals who need to monitor private network traffic distribution. It generally serves as a basic function for the monitoring dashboards of operators’ private network product management platforms, or it can be opened via APIs for private network users or third-party managed platforms to call for secondary development.| + +## ***Summary*** + +In addition to focusing on network performance and faults to ensure network stability, private network users also need to monitor business operation status and identify potential performance bottlenecks. Although the developing network slicing technology provides service assurance for key enterprise services, in practice, network traffic analysis enables private network users to clarify the actual load of various services during different time periods, which is beneficial for accurately determining the upper and lower bandwidth limits required by the services. diff --git a/original/NetworkInsights/documentation/SupportingDocuments/README.MD b/original/NetworkInsights/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/NetworkInsights/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/NetworkSliceBooking/README.md b/original/NetworkSliceBooking/README.md new file mode 100644 index 0000000000000000000000000000000000000000..04a0faf5cb69334a4e1a8cb77243676beb680e9a --- /dev/null +++ b/original/NetworkSliceBooking/README.md @@ -0,0 +1,56 @@ + + + + + + + + + +# NetworkSliceBooking + +Sandbox API Repository to describe, develop, document, and test the NetworkSliceBooking Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/rDPe) + +## Scope +* Service APIs for “Network Slice Booking” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * reserve, dynamically provisioning, query, dynamically delete a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations. + * manage user subscription to the network slices. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: January 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest pre-release is [r2.1](https://github.com/camaraproject/NetworkSliceBooking/releases/tag/r2.1), with the following API versions: + * **network-slice-booking v0.2.0-rc.1** + [[YAML]](https://github.com/camaraproject/NetworkSliceBooking/blob/r2.1/code/API_definitions/network-slice-booking.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-booking.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-booking.yaml) + * **network-slice-assignment v0.1.0-rc.1** + [[YAML]](https://github.com/camaraproject/NetworkSliceBooking/blob/r2.1/code/API_definitions/network-slice-assignment.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-assignment.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NetworkSliceBooking/r2.1/code/API_definitions/network-slice-assignment.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NetworkSliceBooking/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NetworkSliceBooking/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NetworkSliceBooking/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Fridays 16:00 CST / 10:00 CEST + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92204181217?password=7ef83098-28d4-417c-95bc-3f0ab7904c8f) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/NetworkSliceBooking) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/NetworkSliceBooking/code/API_definitions/network-slice-assignment.yaml b/original/NetworkSliceBooking/code/API_definitions/network-slice-assignment.yaml new file mode 100644 index 0000000000000000000000000000000000000000..b882a9e62b561afa228e1806fa00ca1a6ddf0e28 --- /dev/null +++ b/original/NetworkSliceBooking/code/API_definitions/network-slice-assignment.yaml @@ -0,0 +1,1518 @@ +openapi: 3.0.3 +info: + title: Network Slice Assignment + description: | + This API enables the assignment and release of the device to an existing network slice, as well as retrieving information about devices assigned to a slice or slices assigned to a device. + + This API works with the Network Slice Booking API, which is responsible for creating and managing network slices. The Network Slice Assignment API allows API consumers to manage user subscription to the network slices. + + # Functionality + The Network Slice Assignment API provides the following functionalities: + - **Assign Device**: Allows the API consumer to assign a device to an existing network slice, ensuring that the number of devices does not exceed the maximum defined in the slice QoS profile. + - **Release Device**: Enables the API consumer to release a device from an existing network slice. + - **Get Assigned Devices**: Retrieves information about devices currently assigned to a specific network slice. + - **Retrieve Slices by Device**: Retrieves the list of network slices to which a specific device is assigned. + + # Terms and Definitions + + * **Notification Sink and Token**: + API consumers can provide a notification sink URL and an optional sink credential when assigning a device to a slice. The notification sink is the URL where the API response will be asynchronously delivered, using the HTTP protocol. The sink credential provides authentication or authorization information necessary to enable delivery of events to the target. + + # Parameters + + * **sliceQosProfile**: A set of quality of service parameters that define the requirements for the network slice. It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + * **sliceId**: A unique identifier for a network slice, obtained from the createSlice operation of the Network Slice Booking API. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkSliceBooking +servers: + - url: "{apiRoot}/network-slice-assignment/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Slice Assignment + description: Manage Network Slice Assignment +paths: + /slices/{sliceId}/devices: + post: + tags: + - Network Slice Assignment + summary: Assign a device to a network slice + description: | + Assign a device to an existing network slice. The number of devices assigned to the slice must not exceed the maximum number defined in the slice QoS profile. + - If the assignment operation is successful, the response will indicate the status as `SUCCESS`. + - If the number of devices exceeds the maximum allowed for the slice, the response will indicate the status as `FAILURE` with statusInfo as `MAX_DEVICES_EXCEEDED`. + - If the device is already assigned to the slice, the response will indicate the status as `FAILURE` with statusInfo as `DEVICE_ALREADY_ASSIGNED`. + - If the assignment operation is still in progress, the response will indicate the status as `PENDING`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + operationId: assignDevice + security: + - openId: + - network-slice-assignment:devices:assign + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to assign a device to a network slice + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceInput" + examples: + ASSIGN_DEVICE_INPUT_ALL: + $ref: "#/components/examples/ASSIGN_DEVICE_INPUT_ALL" + ASSIGN_DEVICE_INPUT_NUMBER: + $ref: "#/components/examples/ASSIGN_DEVICE_INPUT_NUMBER" + required: true + callbacks: + networkSliceAssignmentSinkCallback: + "{request.body#/sink}": + post: + tags: + - Network Slice Assignment Callback + summary: Network slice assignment callback + description: Callback for network slice assignment events + operationId: postNetworkSliceAssignmentNotification + requestBody: + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + ASSIGNMENT_COMPLETED_EVENT: + $ref: "#/components/examples/ASSIGNMENT_COMPLETED_EVENT" + ASSIGNMENT_DEVICE_EXCEED_EVENT: + $ref: "#/components/examples/ASSIGNMENT_DEVICE_EXCEED_EVENT" + required: true + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: The result of the device assignment operation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInfo" + examples: + ASSIGN_DEVICE_SUCCESSFUL: + $ref: "#/components/examples/ASSIGN_DEVICE_SUCCESSFUL" + ASSIGN_DEVICE_FAILURE_EXCEEDED: + $ref: "#/components/examples/ASSIGN_DEVICE_FAILURE_EXCEEDED" + ASSIGN_DEVICE_ALREADY_ASSIGNED: + $ref: "#/components/examples/ASSIGN_DEVICE_ALREADY_ASSIGNED" + ASSIGN_DEVICE_SLICE_NOT_FOUND: + $ref: "#/components/examples/ASSIGN_DEVICE_SLICE_NOT_FOUND" + ASSIGN_DEVICE_UNKNOWN_ERROR: + $ref: "#/components/examples/ASSIGN_DEVICE_UNKNOWN_ERROR" + ASSIGN_DEVICE_PENDING: + $ref: "#/components/examples/ASSIGN_DEVICE_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Network Slice Assignment + summary: Get devices assigned to a network slice + description: | + Get information about devices assigned to an existing network slice. + operationId: getDevices + security: + - openId: + - network-slice-assignment:devices:get + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about active slice + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceDevices" + examples: + GET_DEVICES_SUCCESSFUL: + $ref: "#/components/examples/GET_DEVICES_SUCCESSFUL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + /slices/{sliceId}/release: + post: + tags: + - Network Slice Assignment + summary: Release a device from an existing network slice + description: | + Release a device from an existing network slice. + - If the release operation is successful, the response will indicate the status as `SUCCESS` with statusInfo as `RELEASE_COMPLETED`. + - If the device is not assigned to the slice, the response will indicate the status as `FAILURE` with statusInfo as `DEVICE_ALREADY_RELEASED`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + operationId: releaseDevice + security: + - openId: + - network-slice-assignment:devices:delete + parameters: + - $ref: "#/components/parameters/sliceId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to release a device from a network slice + content: + application/json: + schema: + $ref: "#/components/schemas/ReleaseDeviceInput" + examples: + RELEASE_DEVICE_INPUT_ALL: + $ref: "#/components/examples/RELEASE_DEVICE_INPUT_ALL" + RELEASE_DEVICE_INPUT_NUMBER: + $ref: "#/components/examples/RELEASE_DEVICE_INPUT_NUMBER" + required: true + responses: + "200": + description: The result of the device release operation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceReleaseInfo" + examples: + RELEASE_DEVICE_SUCCESSFUL: + $ref: "#/components/examples/RELEASE_DEVICE_SUCCESSFUL" + RELEASE_DEVICE_ALREADY_RELEASED: + $ref: "#/components/examples/RELEASE_DEVICE_ALREADY_RELEASED" + RELEASE_DEVICE_SLICE_NOT_FOUND: + $ref: "#/components/examples/RELEASE_DEVICE_SLICE_NOT_FOUND" + RELEASE_DEVICE_UNKNOWN_ERROR: + $ref: "#/components/examples/RELEASE_DEVICE_UNKNOWN_ERROR" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /retrieve-slices: + post: + tags: + - Network Slice Assignment + summary: Retrieve all network slices by device + description: | + Retrieve the list of network slices to which a device is assigned. + operationId: retrieveSlicesByDevice + security: + - openId: + - network-slice-assignment:devices:retrieve + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve slices by device + content: + application/json: + schema: + $ref: "#/components/schemas/Device" + examples: + RETRIEVE_INPUT_PHONENUMBER: + $ref: "#/components/examples/RETRIEVE_INPUT_PHONENUMBER" + required: true + responses: + "200": + description: List of slices the device is assigned + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrievedSlicesOutput" + examples: + RETRIEVE_SUCCESSFUL: + $ref: "#/components/examples/RETRIEVE_SUCCESSFUL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + sliceId: + name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SliceId: + description: Slice ID in UUID format + type: string + format: uuid + DeviceInput: + description: | + Request to add device to a slice + **NOTES:** + - It is the responsibility of the API consumer to ensure that the identifiers they are using are associated with the same device. If unable to do that, only a single identifier SHOULD be provided to the API provider. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options. The API Consumer can provide multiple identifiers to ensure compatibility across different network operators. In this case, the API Provider will use one of the identifiers for the API logic without performing any matching checks among the provided identifiers. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Address" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@example.com" + + DeviceIpv4Address: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Address" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Address" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Address: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ReleaseDeviceInput: + description: Request to release a device from a slice + type: object + properties: + device: + $ref: "#/components/schemas/Device" + required: + - device + DeviceAssignmentInfo: + description: | + Information about the device assignment operation returned in the response. + - If more than one type of device identifier is provided in the request, only one identifier will be returned. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + sliceId: + $ref: "#/components/schemas/SliceId" + status: + $ref: "#/components/schemas/AssignmentStatus" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - sliceId + - status + AssignmentStatus: + description: | + Status of the device assignment operation + * `SUCCESS` - Device is successfully assigned to the slice + * `FAILURE` - Device fail to assign to the slice + * `PENDING` - The assignment operation is still in progress + type: string + enum: + - SUCCESS + - FAILURE + - PENDING + AssignmentStatusInfo: + description: | + Additional information about the assignment status + * `ASSIGNMENT_COMPLETED` - The assignment operation has been completed + * `MAX_DEVICES_EXCEEDED` - The number of devices exceeds the maximum allowed for the slice + * `DEVICE_ALREADY_ASSIGNED` - Device is already assigned to the slice + * `SLICE_NOT_FOUND` - The specified sliceId does not exist + * `ASSIGNMENT_UNKNOWN_ERROR` - The assignment operation failed due to an unknown error + * `VALIDATION_PENDING` - The assignment request is pending for validation and verification + type: string + enum: + - ASSIGNMENT_COMPLETED + - MAX_DEVICES_EXCEEDED + - DEVICE_ALREADY_ASSIGNED + - SLICE_NOT_FOUND + - ASSIGNMENT_UNKNOWN_ERROR + - VALIDATION_PENDING + DeviceReleaseInfo: + description: | + Information about the device release from network slice operation returned in the response. + - If more than one type of device identifier is provided in the request, only one identifier will be returned. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + sliceId: + $ref: "#/components/schemas/SliceId" + status: + $ref: "#/components/schemas/ReleaseStatus" + statusInfo: + $ref: "#/components/schemas/ReleaseStatusInfo" + required: + - sliceId + - status + ReleaseStatus: + description: | + Status of the device release operation + * `SUCCESS` - Device is successfully released from the slice + * `FAILURE` - Device fail to release from the slice + type: string + enum: + - SUCCESS + - FAILURE + ReleaseStatusInfo: + description: | + Additional information about the release status + * `RELEASE_COMPLETED` - The release operation has been completed + * `DEVICE_ALREADY_RELEASED` - Device is already released from the slice + * `SLICE_NOT_FOUND` - The specified sliceId does not exist + * `RELEASE_UNKNOWN_ERROR` - The release operation failed due to an unknown error + type: string + enum: + - RELEASE_COMPLETED + - DEVICE_ALREADY_RELEASED + - SLICE_NOT_FOUND + - RELEASE_UNKNOWN_ERROR + RetrievedSlicesOutput: + description: Response containing slices assigned to a device + type: object + properties: + sliceList: + type: array + items: + $ref: "#/components/schemas/SliceInfo" + minItems: 0 + + SliceDevices: + description: Information about devices assigned to a slice + type: object + properties: + deviceList: + type: array + items: + $ref: "#/components/schemas/Device" + minItems: 0 + sliceInfo: + $ref: "#/components/schemas/SliceInfo" + required: + - deviceList + - sliceInfo + SliceInfo: + description: Slice related information. + allOf: + - $ref: "#/components/schemas/SliceAttributes" + - type: object + properties: + sliceId: + $ref: "#/components/schemas/SliceId" + required: + - sliceId + SliceAttributes: + description: Attributes defining the characteristics of the slice + type: object + properties: + serviceTime: + description: | + serviceTime is a period during which the network slice will be reserved. + It is defined by a start time and an end time. + allOf: + - $ref: "#/components/schemas/TimePeriod" + serviceArea: + description: | + serviceArea is a geographical area where the network slice will be reserved. + It can be defined as a circle or a polygon. + allOf: + - $ref: "#/components/schemas/Area" + sliceQosProfile: + description: | + sliceQosProfile is a set of quality of service parameters that define the requirements for the network slice. + It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + allOf: + - $ref: "#/components/schemas/SliceQosProfile" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - serviceTime + - serviceArea + - sliceQosProfile + + SliceQosProfile: + description: | + Quality of service for the network slice. + It includes a set of predefined network slice performance characteristics. + type: object + properties: + maxNumOfDevices: + description: | + maxNumOfDevices is a maximum number of devices that can be connected to the slice + allOf: + - $ref: "#/components/schemas/NumberOfDevices" + downStreamRatePerDevice: + description: | + downStreamRatePerDevice is the maximum downstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + upStreamRatePerDevice: + description: | + upStreamRatePerDevice is the maximum upstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + downStreamDelayBudget: + description: | + downStreamDelayBudget is the maximum allowable downlink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + upStreamDelayBudget: + description: | + upStreamDelayBudget is the maximum allowable uplink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + + + Duration: + description: Specification of duration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#appendix-A) for duration. + type: object + properties: + value: + description: Length of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + NumberOfDevices: + type: integer + example: 5 + description: Maximum number of devices that is allowed to be connected to the network at any point in time. + + format: int32 + minimum: 1 + maximum: 20 + + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-02T12:00:00Z" + required: + - startDate + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 31.22529 + longitude: 121.48905 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + type: string + description: The type of the event + enum: + - "org.camaraproject.network-slice-assignment.v0.status-changed" + minLength: 25 + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: type + mapping: + org.camaraproject.network-slice-assignment.v0.status-changed: "#/components/schemas/AssignmentDeviceEvent" + + AssignmentDeviceEvent: + description: Event to notify about device assignment status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + description: Event details depending on the event type + allOf: + - $ref: "#/components/schemas/DeviceAssignmentInfo" + required: + - data + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + WARN: This optional field in CloudEvents specification is required in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + NetworkSliceBooking422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - NETWORK_SLICE_BOOKING.RESOURCES_NOT_APPLICABLE + examples: + NETWORK_SLICE_BOOKING_422_RESOURCES_NOT_APPLICABLE: + description: Request cannot be processed due to business logic validation failure, e.g. service area is not supported or resources are insufficient + value: + status: 422 + code: NETWORK_SLICE_BOOKING.RESOURCES_NOT_APPLICABLE + message: The request resources are not applicable for slice creation. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Quota Exceed or Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ASSIGNMENT_COMPLETED_EVENT: + summary: Assignment Completed Event + description: Example of notification event sent when device assignment is completed + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-assignment.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + ASSIGNMENT_DEVICE_EXCEED_EVENT: + summary: Assignment Device Exceed Event + description: Example of notification event sent when device assignment fails due to maximum devices exceeded + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-assignment.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "MAX_DEVICES_EXCEEDED" + ASSIGN_DEVICE_INPUT_ALL: + summary: Assign device - All Identifiers + description: Example of request to assign a device to a network slice using all identifiers + value: + device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + sink: + "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + ASSIGN_DEVICE_INPUT_NUMBER: + summary: Assign device - Phone Number Identifier + description: Example of request to assign a device to a network slice using phone number identifier + value: + device: + phoneNumber: "+123456789" + sink: + "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + ASSIGN_DEVICE_SUCCESSFUL: + summary: Assignment Successful + description: Example of successful response for assigning a device to a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + ASSIGN_DEVICE_FAILURE_EXCEEDED: + summary: Assignment Failure for DeviceNum Exceeded + description: Example of failure response for assigning a device to a network slice request due to maximum devices exceeded + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "MAX_DEVICES_EXCEEDED" + ASSIGN_DEVICE_ALREADY_ASSIGNED: + summary: Assignment Failure for Device Already Assigned + description: Example of failure response for assigning a device to a network slice request due to device already assigned + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "DEVICE_ALREADY_ASSIGNED" + ASSIGN_DEVICE_SLICE_NOT_FOUND: + summary: Assignment Failure for Slice Not Found + description: Example of failure response for assigning a device to a network slice request due to sliceId not found + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "SLICE_NOT_FOUND" + ASSIGN_DEVICE_UNKNOWN_ERROR: + summary: Assignment Failure for Unknown Error + description: Example of failure response for assigning a device to a network slice request due to unknown error + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "ASSIGNMENT_UNKNOWN_ERROR" + ASSIGN_DEVICE_PENDING: + summary: Assignment Pending + description: Example of pending response for assigning a device to a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + RELEASE_DEVICE_INPUT_NUMBER: + summary: Release device - Phone Number Identifier + description: Example of request to assign a device to a network slice using phone number identifier + value: + device: + phoneNumber: "+123456789" + RELEASE_DEVICE_INPUT_ALL: + summary: Release device - All Identifiers + description: Example of request to assign a device to a network slice using all identifiers + value: + device: + phoneNumber: "+123456789" + networkAccessIdentifier: "123456789@domain.com" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + RELEASE_DEVICE_SUCCESSFUL: + summary: Release Successful + description: Example of successful response for releasing a device from a network slice request + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "SUCCESS" + statusInfo: "RELEASE_COMPLETED" + RELEASE_DEVICE_ALREADY_RELEASED: + summary: Release Failure for Device Already Released + description: Example of failure response for releasing a device from a network slice request due to device already not assigned to the slice + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "DEVICE_ALREADY_RELEASED" + RELEASE_DEVICE_SLICE_NOT_FOUND: + summary: Release Failure for Slice Not Found + description: Example of failure response for releasing a device from a network slice request due to sliceId not found + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "SLICE_NOT_FOUND" + RELEASE_DEVICE_UNKNOWN_ERROR: + summary: Release Failure for Unknown Error + description: Example of failure response for releasing a device from a network slice request due to unknown error + value: + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + device: + phoneNumber: "+123456789" + status: "FAILURE" + statusInfo: "RELEASE_UNKNOWN_ERROR" + GET_DEVICES_SUCCESSFUL: + summary: Get Devices Successful + description: Example of successful response for getting devices assigned to a network slice request + value: + deviceList: + - device: + phoneNumber: "+123456789" + - device: + phoneNumber: "+987654321" + sliceInfo: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + RETRIEVE_INPUT_PHONENUMBER: + summary: Retrieve Slice Info - Phone Number Identifier + description: Example of request to retrieve network slice info using phone number identifier + value: + device: + phoneNumber: "+123456789" + RETRIEVE_SUCCESSFUL: + summary: Retrieve Slice Info Successful + description: Example of successful response for retrieving network slice info request + value: + sliceList: + - serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" diff --git a/original/NetworkSliceBooking/code/API_definitions/network-slice-booking.yaml b/original/NetworkSliceBooking/code/API_definitions/network-slice-booking.yaml new file mode 100644 index 0000000000000000000000000000000000000000..db7cda78851bc6bd5f57d37dc8fc9b37fcb53c68 --- /dev/null +++ b/original/NetworkSliceBooking/code/API_definitions/network-slice-booking.yaml @@ -0,0 +1,1113 @@ +openapi: 3.0.3 +info: + title: Network Slice Booking + description: | + The Network Slice Booking (NSB) API provides programmable interface for developers to reserve a slice resource of a selected area within a period, and manage device access control as needed. + For specific details, please refer to [Network Slice Booking API Design.md](https://github.com/camaraproject/NetworkSliceBooking/blob/main/documentation/API_documentation/Network_Slice_Booking_API_Design.md). + + # Introduction + + This API allows the API consumer to book the availability of a network slice, specifying the service time, service area, and quality of service (QoS) profile. + It checks whether the requested QoS profile can be guaranteed for the indicated time and area, and, if so, it reserves the network slice accordingly, and monitors that the slice delivers the QoS profile. The latter process is known as Service Level Agreement (SLA) monitoring. + + The API consumer can also retrieve information about an existing slice or delete a slice. + + # API functionality + + The API provides the following functionality: + - Create a new network slice, specifying the service time, service area, and QoS profile. + - Retrieve information about an existing slice, including the service time, service area, and QoS profile. + - Delete an existing slice. + + # Request Parameters Definition: + * **serviceTime**: is defined by a start time and an end time, which indicates the period during which the network slice will be reserved. + * **serviceArea**: can be defined as a circle or a polygon, allowing for flexible geographical coverage. + * **sliceQosProfile**: includes parameters such as maximum number of devices, downstream and upstream rate per device, and packet delay budget. + * **sliceId**: is a unique identifier for the network slice, which is returned when a slice is created and used to retrieve or delete the slice later. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Network Slice Booking API does not involve the input and output of user personal data. Therefore, the access to Network Slice Booking API is defined as `Client Credentials - 2-legged`. Please refer to [Identify and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: "0.7" + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NetworkSliceBooking +servers: + - url: "{apiRoot}/network-slice-booking/vwip" + variables: + apiRoot: + default: http://localhost:9100 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Network Slice Booking + description: Manage Network Slice Booking +paths: + /slices: + post: + tags: + - Network Slice Booking + summary: Creates a new network slice + description: | + Create a new network slice with the expected service time, service area, and QoS profile. + + NOTES: + - If newtwork slice creation is successful, the API consumer will receive a response with code `201 - Created` and a slice ID. + - If requested service area is not supported, the API consumer will receive a response with code `422 - NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED`. + - If the left resources are not sufficient for the requested slice resources, the API consumer will receive a response with code `422 - NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT`. + operationId: createSlice + security: + - openId: + - network-slice-booking:slices:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new network slice + content: + application/json: + schema: + $ref: "#/components/schemas/SliceAttributes" + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + required: true + callbacks: + networkSliceBookingSinkCallback: + "{request.body#/sink}": + post: + tags: + - Network Slice Booking Callback + summary: Network slice booking callback + description: Callback for network slice booking events + operationId: postNetworkSliceBookingNotification + requestBody: + description: Network slice booking event notification + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + SLICE_CREATED_EVENT_CIRCLE: + $ref: "#/components/examples/SLICE_CREATED_EVENT_CIRCLE" + SLICE_CREATED_EVENT_POLYGON: + $ref: "#/components/examples/SLICE_CREATED_EVENT_POLYGON" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Slice created successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceInfo" + examples: + RESPONSE_CIRCLE: + $ref: "#/components/examples/RESPONSE_CIRCLE" + RESPONSE_POLYGON: + $ref: "#/components/examples/RESPONSE_POLYGON" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "422": + $ref: "#/components/responses/NetworkSliceBooking422" + "429": + $ref: "#/components/responses/Generic429" + + /slices/{sliceId}: + delete: + tags: + - Network Slice Booking + summary: Delete a network slice + description: | + Release slice resources related to sliceId. + + NOTES: + - The deletion operation takes effect immediately, e.g. if the slice is deleted before the end of the service time, the service will end ahead of the scheduled time. + - If the slice is deleted, the API consumer will not be able to retrieve information about the slice. + - The deletion operation is idempotent, meaning that if the slice is already deleted, the API consumer will receive a response with code `204 - No Content`. + operationId: deleteSlice + security: + - openId: + - network-slice-booking:slices:delete + parameters: + - name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Slice deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + get: + tags: + - Network Slice Booking + summary: Get network slcie booking information + description: | + Querying for network slcie booking resource information details. + + NOTES: + - According to sliceId, the API consumer can retrieve information about an existing slice, including the service time, service area, and QoS profile. + - If the slice is deleted, the API consumer will receive a response with code `404 - Not Found`. + operationId: getSlice + security: + - openId: + - network-slice-booking:slices:get + parameters: + - name: sliceId + in: path + description: Slice ID that was obtained from the createSlice operation + required: true + schema: + $ref: "#/components/schemas/SliceId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about network slice booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SliceInfo" + examples: + RESPONSE_CIRCLE: + $ref: "#/components/examples/RESPONSE_CIRCLE" + RESPONSE_POLYGON: + $ref: "#/components/examples/RESPONSE_POLYGON" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + description: Bearer authentication for notifications + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SliceId: + description: Slice ID in UUID format + type: string + format: uuid + SliceInfo: + description: Slice related information. + allOf: + - $ref: "#/components/schemas/SliceAttributes" + - type: object + properties: + sliceId: + $ref: "#/components/schemas/SliceId" + required: + - sliceId + + SliceAttributes: + description: Attributes defining the characteristics of the slice + type: object + properties: + serviceTime: + description: | + serviceTime is a period during which the network slice will be reserved. + It is defined by a start time and an end time. + allOf: + - $ref: "#/components/schemas/TimePeriod" + serviceArea: + description: | + serviceArea is a geographical area where the network slice will be reserved. + It can be defined as a circle or a polygon. + allOf: + - $ref: "#/components/schemas/Area" + sliceQosProfile: + description: | + sliceQosProfile is a set of quality of service parameters that define the requirements for the network slice. + It includes parameters such as maximum number of devices, downlink and uplink throughput per device, and latency requirements. + allOf: + - $ref: "#/components/schemas/SliceQosProfile" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - serviceTime + - serviceArea + - sliceQosProfile + + SliceQosProfile: + description: | + Quality of service for the network slice. + It includes a set of predefined network slice performance characteristics. + type: object + properties: + maxNumOfDevices: + description: | + maxNumOfDevices is a maximum number of devices that can be connected to the slice + allOf: + - $ref: "#/components/schemas/NumberOfDevices" + downStreamRatePerDevice: + description: | + downStreamRatePerDevice is the maximum downstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + upStreamRatePerDevice: + description: | + upStreamRatePerDevice is the maximum upstream rate allowed for each device connected to the slice. + It indicates the individual device capability required for the slice. + allOf: + - $ref: "#/components/schemas/Rate" + downStreamDelayBudget: + description: | + downStreamDelayBudget is the maximum allowable downlink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + upStreamDelayBudget: + description: | + upStreamDelayBudget is the maximum allowable uplink packet transmission latency (millisecond). + By limiting the delay, the network can provide an acceptable level of performance for various services, such as voice calls, video streaming, and data. + allOf: + - $ref: "#/components/schemas/Duration" + + + Duration: + description: Specification of duration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#appendix-A) for duration. + type: object + properties: + value: + description: Length of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + NumberOfDevices: + type: integer + example: 5 + description: Maximum number of devices that is allowed to be connected to the network at any point in time. + + format: int32 + minimum: 1 + maximum: 20 + + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-01T12:00:00Z" + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2024-06-02T12:00:00Z" + required: + - startDate + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 31.22529 + longitude: 121.48905 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + required: + - status + - code + - message + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + type: string + description: The type of the event + enum: + - "org.camaraproject.network-slice-booking.v0.status-changed" + minLength: 25 + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: type + mapping: + org.camaraproject.network-slice-booking.v0.status-changed: "#/components/schemas/SliceCreatedEvent" + + SliceCreatedEvent: + description: Event to notify a slice creation status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + description: Event details depending on the event type + allOf: + - $ref: "#/components/schemas/SliceInfo" + required: + - data + + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + WARN: This optional field in CloudEvents specification is required in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Specified slice resource is not found based on the sliceId + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + NetworkSliceBooking422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED + - NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT + examples: + NETWORK_SLICE_BOOKING_422_SERVICE_AREA_NOT_SUPPORTED: + description: Business logic exception use when the requested service area is not supported + value: + status: 422 + code: NETWORK_SLICE_BOOKING.SERVICEAREA_NOT_SUPPORTED + message: The requested service area is not supported. + NETWORK_SLICE_BOOKING_422_RESOURCES_INSUFFICIENT: + description: Business logic exception use when the left resources are not sufficient for the requested slice resources + value: + status: 422 + code: NETWORK_SLICE_BOOKING.RESOURCES_INSUFFICIENT + message: The left resources are not sufficient for the requested slice resources. + Generic429: + description: Quota Exceed or Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + RETRIEVAL_CIRCLE: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + RETRIEVAL_POLYGON: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + RESPONSE_CIRCLE: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + RESPONSE_POLYGON: + value: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + SLICE_CREATED_EVENT_CIRCLE: + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-booking.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + SLICE_CREATED_EVENT_POLYGON: + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + type: "org.camaraproject.network-slice-booking.v0.status-changed" + datacontenttype: "application/json" + time: "2024-06-01T12:00:00Z" + data: + serviceTime: + startDate: "2024-06-01T12:00:00Z" + endDate: "2024-06-02T12:00:00Z" + serviceArea: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + sliceQosProfile: + maxNumOfDevices: 5 + downStreamRatePerDevice: + value: 10 + unit: bps + upStreamRatePerDevice: + value: 10 + unit: bps + downStreamDelayBudget: + value: 12 + unit: Milliseconds + upStreamDelayBudget: + value: 12 + unit: Milliseconds + sliceId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" diff --git a/original/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom.md b/original/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom.md new file mode 100644 index 0000000000000000000000000000000000000000..d6535c8ca514d38feb96b9d5e23da7dd66c15dff --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/APIproposal_NetworkSlicing_ChinaUnicom.md @@ -0,0 +1,13 @@ +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API family owner | China Unicom, China Telecom, Huawei | +| API family supporter | China Mobile, China Unicom, China Telecom, Huawei, TBD | +| API summary | There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.

                                                    Proposed API Definitions
                                                    -Input Parameters:
                                                    Service Time:Start Time ~ End Time
                                                    Service Area:Geographical area (Point, Line, Area)
                                                    Guaranteed terminals:Number of terminals
                                                    SLA Targets:SLA KPIs (such as DL/UL Avg Throughput, Latency)

                                                    -Output Parameters:
                                                    Slice Reservation Result: network slice reservation success (with Slice ID) or failure.

                                                    An example: a developer may use this API to book a network slice with expected service time, expected service area, expected guaranteed numbers of terminals and expected SLA targets for 2 hours to 2 weeks in advance for some scheduled events like a live stream festival scheduled in some place.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| +| YAML code available? | No, needs to be provided in yaml. | +| Validated in lab/productive environments? | Yes, in productive network. | +| Validated with real customers? | Yes | +| Validated with operators? | Yes , 3 operators participated in the evaluations. | +| Others | More details can be refered in PPT. | diff --git a/original/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story.md b/original/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..f4f1099e5f9b580f041606ba2bdfbaaf05fb3a22 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/NSA_User_Story.md @@ -0,0 +1,50 @@ +# Network Slice Assignment (NSA) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API summary | **Overview**: There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area.
                                                    **Correlation with network-slice-booking API**: The Network Slice Booking API provides such abilities for OTT developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on. Network Slice Assignment API serves as a key user touchpoint in the network slicing service process, enabling OTT service providers to dynamically and in real-time bind their end-users to the network slices that have successfully reserved.This API accomplishes the final step of transformation from "activating slices for business" to "enabling users to experience slices".
                                                    **Network Slice Assignment API**: It allows developers to assign/release users to/from reserved slices, as well as provides functionalities to query assigned slices through user devices and retrieve the list of users currently assigned to a reserved slice by the slice identifier.

                                                    Proposed API Definitions
                                                    -Input Parameters:
                                                    Device: device identifiers (ipv4Address, ipv6Address, phoneNumber, networkAccessIdentifier)
                                                    SliceId: network slice Identifier

                                                    -Output Parameters:
                                                    Slice Assignment Result: device assigned to network slice success or failure (status and reason).

                                                    An example: An OTT service provider (e.g. a live streaming platform) has completed network slice reservation preparations for an upcoming live streaming event. To ensure a high-quality live streaming experience for users, the following steps need to be completed.
                                                    Reservation Preparation: The OTT service provider (e.g., a live streaming platform) successfully provisions a network slice with high uplink bandwidth and low-latency guarantees in advance for an upcoming "online live streaming event" through the `network-slice-booking` API, obtaining a unique `slice_id`.
                                                    User Trigger: Influencer Companies or studios subscribe to the "Dedicate/Premium Streaming Service" on the live streaming platform.
                                                    API Call: The live streaming app calls the `network-slice-assignment` API in the background to associate the terminal information (e.g., mobile number, IP address) of the influencer company/studio with the previously reserved `slice_id`.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| + +## ***Summary*** + +There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slice Booking API provides such abilities for OTT developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.
                                                    The Network Slice Assignment API then lets them dynamically assign end-users to these reserved slices, delivering the guaranteed experience. It allows developers to assign/release users to/from reserved slices, as well as provides functionalities to query assigned slices through user devices and retrieve the list of users currently assigned to a reserved slice by the slice identifier. + +## ***Scenarios - Assignment Scenario 1*** + +**Operators:** + +Telecom provides Network Slice Assignment API for enterprise customer. Assigning slice resources to end-users enables to provide guaranteed network services. + +**API Consumers:** + +OTT as API consumer. Eg: Tiktok +TitTok can Assign the ordered slice resources for end users by this API, achieving the provision of network guarantee services for its end users + +**API End Users:** + +OTT Customers Eg: Tiktok Influencer Studios + +1. Influencers Companies or Studios may order "Dedicate/Premium Streaming Service" provided by Tiktok. +2. Tiktok then help Influencer Companies on binding their devices into the Slice by calling the Network Slice Assignment APIs. + +## ***Scenarios - Assignment Scenario 2*** + +**Operators:** + +Telecom provides Network Slice Assignment API for enterprise customer. Assigning slice resources to end-users enables to provide guaranteed network services. + +**API Consumers:** + +Enterprises Developer. Eg: TV Station Developer + +1. TV Stations usually have grand TV Live Streaming Business. They need Slice Assurance Services to assure that they have dedicated network resources for their streaming. +2. TV Stations APP developer call Network Slice Assignment API provided by Telecom NaaS Platform/Aggregator Platform directly to make it "Streaming Assurance" function on the APP. + +**API End Users:** + +Video Consumer. Eg: Fans watching the game + +1. Fans watching the game can order "Dedicate/Premium Streaming Service" provided by TV App. +2. Fans watching the game can Enjoy a high-definition and smooth competition experience binding their devices into the Slice by calling the Network Slice Assignment APIs. \ No newline at end of file diff --git a/original/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story.md b/original/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..dffa83bf9087064d2685e73a1fa73076eef3e73f --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/NSB_User_Story.md @@ -0,0 +1,34 @@ +# Network Slice Booking (NSB) API User Story + +| **Field** | Description | +| ---- | ----- | +| API family name | Network Slicing API | +| API summary | There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on.

                                                    Proposed API Definitions
                                                    -Input Parameters:
                                                    Service Time:Start Time ~ End Time
                                                    Service Area:Geographical area (Point, Line, Area)
                                                    Guaranteed terminals:Number of terminals
                                                    SLA Targets:SLA KPIs (such as DL/UL Avg Throughput, Latency)

                                                    -Output Parameters:
                                                    Slice Reservation Result: network slice reservation success (with Slice ID) or failure.

                                                    An example: a developer may use this API to book a network slice with expected service time, expected service area, expected guaranteed numbers of terminals and expected SLA targets for 2 hours to 2 weeks in advance for some scheduled events like a live stream festival scheduled in some place.| +| Technical viability | This API requires the availability of RAN slicing, UDM, PCF, and network slicing management services as expressed in 3GPP TS 28.531 (network slice provisioning operations), TS 28.541 (Information model definitions for network slice NRM) standards.| +| Commercial viability | Network Slicing has been commercialized in many fields. Static Slicing has helped operators monetized. Dynamic Slicing is on the way of huge potential value. It’s especially valuable in influencer live video stream, new media, power fiber scenario, industry fileds, there already appear many commercial use cases.| + +## ***Summary*** + +There are emerging requirements in high-rate time-critical applications in the areas of Cloud-gaming, AR/VR, Live Video Streaming, Real-time Multi-Media etc through mobile networks. The on-demand network slicing service technology can provide a network slice reservation method for such scenarios to meet the SLA assurance expected by developers for a specific time period and a dedicated service area. The Network Slicing API provides such abilities for developers to reserve, dynamically provisioning, query, dynamically destroy a slice with customized SLA assurance capabilities, customized service duration, expected slice covered locations and so on. + +## ***Scenarios - Booking Scenario 1*** + +**Operators:** + +Telecom Provide Network Slice Booking API, Providing enterprise customers with the ability to order network slice resources at designated times in designated areas, laying the foundation for subsequent enterprise customer service to end users. + +**API Consumers:** + +OTT as API consumer. Eg: Tiktok +TitTok can order network slicing resources for a specific area at a specific time by this API, These resources lay the foundation for providing network guarantee services to end users in the future. + +## ***Scenarios - Booking Scenario 2*** + +**Operators:** + +Telecom Provide Network Slice Booking API on NaaS Platform or Aggregator Platform + +**API Consumers:** + +Enterprises Developer. Eg: TV Station Developer +TV Stations APP developer call Network Slice Booking API provided by Telecom NaaS Platform/Aggregator Platform directly to order network slice resources for the TV station. It provide a resource foundation for the "Streaming Assurance" function on the APP \ No newline at end of file diff --git a/original/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design.md b/original/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design.md new file mode 100644 index 0000000000000000000000000000000000000000..00e146e8d23c7aeb474344c3fc693db84ad327e1 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/Network_Slice_Booking_API_Design.md @@ -0,0 +1,80 @@ +# Network Slice Booking API Design + +## **Use Cases** +The business modes of Network Slice Booking can be B2B, B2B2C. + +Note: Currently, we've come across the following business modes, which can be grouped into these 3 in general. If there's any other modes, please do not hesitate to propose. + +**1. Scenario 1 - B2B** + + In brief: toB Enterprise customers come to NaaS Platform, book a slice, telecom operator provide the service. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: Enterprise APP Developer + + End User: toB Enterprise Customer + + Example Use Cases: For enterprise customers, who in the past need to talk to a customer manager, to book a slice service. Now those group of customers may renew, modify, or cancel a slice service within a NaaS Service API call. + + +**2. Scenario 2 - B2B2C** + + In brief: OTT abstract the slice api from NaaS Platform, provide a channel for toC individual customers, to buy a slice from NaaS Plaform. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: APP Developer (eg. OTT) + + Slice Product Provider: APP Developer (eg. OTT) + + End User: toC APP End Users (eg. Individuals / Influencers / Streaming Studios ) + + Example Use Cases: + - OTT call the API from any NaaS Platform, in the way of calling Network Slice Booking API. + - OTT abstract the API, make it a Slice Product, provided to toC customers, who are OTT APP End Users. + - End Users buy the service through the APP. + - OTT transfer the request to NaaS Platform. + - Telecom Operators provide the slice service to End Users directly. + +**3. Scenario3 - B2B2C** + + In brief: OTT buy the slice from NaaS Platform, and resell the slice to toC individual customers. + + API Provided By: Telecom Operator's NaaS Platform, or Aggregator's NaaS Platform + + API Consumer: APP Developer (eg. OTT) + + API Reseller: APP Developer (eg. OTT) + + End User: toC APP End Users (eg. Individuals / Influencers / Streaming Studios ) + + Example Use Cases: + - OTT book slices from any NaaS Platform, in the way of calling Network Slice Booking API. + - OTT may book a bunch of slices of different time and locations at one time. + - Telecom Operators provide slice service for OTT. + - OTT abstract the API to an APP function, and resell the service to End Users. Resell modes depends on OTT itself. + - End Users buy the service from OTT. + + + +## **API Design** + +Generally: Split the slice reservation function and device access control function + - API 1:Reserve a slice resource + - API 2:Device Access Management / Manage the access control of devices to the slice + - Note: Basically there should be a CRUD for "Reserve a Slice Resource" and a CRUD for "Manage the access control of devices to the slice". + + +**API 1:Reserve a slice resource** + - Function: + - Reserve a slice of one selected period and one selected area. + - Device Access Management may happen at any point in time while the resource is in revered-state and in active-state. + + +**API 2:Device Access Management / Manage the access control of devices to the slice** + - Function: + - Allow API caller manage the access control from devices to the slice. + + + diff --git a/original/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist.md b/original/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..4bc61c4cbc183c18b2ac1e02f9b128d265053171 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/network-slice-assignment-API-Readiness-Checklist.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for network-slice-assignment v0.1.0-rc.1 in r2.1 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/network-slice-assignment.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0-rc.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/network-slice-assignment.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory for Network Slicing Assignment](/documentation/API_documentation/NSA_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/535625738/NetworkSliceAssignment+API+description) | | + diff --git a/original/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist.md b/original/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..c37eb94b86e8dac03ea08562c6d52a4dcdea9229 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/API_documentation/network-slice-booking-API-Readiness-Checklist.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for network-slicing-booking v0.2.0-rc.1 in r2.1 + +| Nr | API release assets | alpha | release-candidate | initial
                                                    public | stable
                                                    public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/network-slice-booking.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.4](https://github.com/camaraproject/Commonalities/releases/tag/r3.4) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.2.0-rc.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/network-slice-booking.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory for Network Slicing Booking](/documentation/API_documentation/NSB_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link]( https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81166982/NetworkSliceBooking+API+description) | | + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15.md new file mode 100644 index 0000000000000000000000000000000000000000..a0a9321c1e0ea81444d3a2aeedfdded6dd146350 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-03-15.md @@ -0,0 +1,40 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-03-15 + +*Friday, March 15th, 2024* + +## Attendees (probably incomplete) + +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ludovic (Orange) +* Gregory Liukumovich (Ericsson) +* Kai Zhang (Huawei) +* Ricardo Serrano (Telefonica) +* Rafal Artych (DT) +* Shilpa (DT) +* Thorsten Lohmar (Ericsson) +* Zohaib Khan (CPaaS) +* Guanyu Zhu (Huawei) +* Tanja de Groot (Nokia) +* Christian (Unknown) +* ... + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* v0.1.0 Release scope & timeline +* AOB + +## Issues relevant for v0.1.0 +* Issue#2 Project Initialization https://github.com/camaraproject/NetworkSliceBooking/issues/2 +* Issue#5 Slice Booking API Introduction Documentation https://github.com/camaraproject/NetworkSliceBooking/issues/5 + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, March 29th, 16:00 CST / 9:30 CET +2. Currently, different projects have different release nums. Should we start with v0.1.0? What's the release planning of CAMARA for 2024? +3. Considering about the API name, easy for developers to understand. \ No newline at end of file diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10.md new file mode 100644 index 0000000000000000000000000000000000000000..fd04e85f01551e815bbf0ce7c3b61633ef3b2f40 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-10.md @@ -0,0 +1,35 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Hanbai Wang (China Mobile) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Kai Zhang (Huawei) +* Ricardo Serrano (Telefonica) +* Thorsten Lohmar (Ericsson) +* Masaharu Hattori(KDDI) +* Jing Hao(China Unicom) + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Meeting Schedule Adjust + * Meeting Links are adjusted. Including meeting links. Links of S2C, Region User Count, Network Slice API are split into 3 different meeting links as suggested. + * Meeting times are adjusted. Later the Bi-weekly meeting will start from 4pm CST, 10am CEST. +* Issue#22 API Design + * Currently, WG come across 3 modes of business scenarios. WG call for more ideas the API mode. + * Questions toward the business mode work flow, the OTT roles, the Aggregator roles are clear. B2B, B2B2C, B2C are need to be considered. API need to compatible the all the modes. + * The architecture need to be adjusted. Aggregator need to adjust to the layer above the operator. + * Review comments will be resolved later. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, May 24th, 16:00 CST / 10:00 CET diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24.md new file mode 100644 index 0000000000000000000000000000000000000000..0cd7d68fa2b7e28997c0973a23bcd3c49b295393 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-05-24.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-24 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ricardo Serrano (Telefonica) +* Steve Vickers (Vodafone) +* Thorsten Lohmar (Ericsson) +* Bart van Kaathoven (Ericsson) +* Veerat (Comviva) +* Vidhi Mehta (Comviva) +* Tanja de Groot (Nokia) +* Zach Callahan () + + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Issue#22 API Design + * For the current architecture part: "NaaS Portal" module is not clear, there are some misunderstandings. + * For the Service API part: questions from participant is clarified and aligned. + * Clarifications on participants questions: + * Arrows marked in camara blue are Service API. Arrows marked in black are other APIs. + * API from both Operator and Aggregator Platform, to Developer are CAMARA service api. + * Below the Operator/Aggregator Platform is transformation function. + * Alignments on the following modifications: + * Use "Operator Platform" to substitute "Operator NaaS Portal" expression. + * Refer to CAMARA slides architecture instead. + * Action points: + * Participant will provide architecture reference link under the PR. Modifications on the graph will start. + * Corresponding modifications towards contexts will be conduct after the graph. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, Jun 22th, 16:00 CST / 10:00 CET \ No newline at end of file diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05.md new file mode 100644 index 0000000000000000000000000000000000000000..0cd7d68fa2b7e28997c0973a23bcd3c49b295393 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-05.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-24 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Dan Xu (China Telecom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ricardo Serrano (Telefonica) +* Steve Vickers (Vodafone) +* Thorsten Lohmar (Ericsson) +* Bart van Kaathoven (Ericsson) +* Veerat (Comviva) +* Vidhi Mehta (Comviva) +* Tanja de Groot (Nokia) +* Zach Callahan () + + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Issue#22 API Design + * For the current architecture part: "NaaS Portal" module is not clear, there are some misunderstandings. + * For the Service API part: questions from participant is clarified and aligned. + * Clarifications on participants questions: + * Arrows marked in camara blue are Service API. Arrows marked in black are other APIs. + * API from both Operator and Aggregator Platform, to Developer are CAMARA service api. + * Below the Operator/Aggregator Platform is transformation function. + * Alignments on the following modifications: + * Use "Operator Platform" to substitute "Operator NaaS Portal" expression. + * Refer to CAMARA slides architecture instead. + * Action points: + * Participant will provide architecture reference link under the PR. Modifications on the graph will start. + * Corresponding modifications towards contexts will be conduct after the graph. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, Jun 22th, 16:00 CST / 10:00 CET \ No newline at end of file diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19.md new file mode 100644 index 0000000000000000000000000000000000000000..2e148fa53d419036eea639c603caf6fe8a99f8fb --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2024-07-19.md @@ -0,0 +1,44 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-07-19 + + +*Friday, Jul 19th, 2024* + + +## Attendees +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu(Huawei) +* Thorsten Lohmar (Ericsson) +* Tanja de Groot (Nokia) +* Masaharu Hattori(KDDI) +* Bart van Kaathoven(Ericsson) +* Pedro Bento() + + +## Agenda +* Issue#33 and PR#32 API Yaml update +* Issue#38 discussion - Add an “Area” data-type into CAMARA_common.yaml +* Issue#39 discussion - API BACKLOG - Dedicated Networks: Scope Enhancement proposal +* AOB + + +## Issues Discussions +* Issue#33 and PR#32 API Yaml update + * Still modify the yaml file based on previous meeting discussion and It's not finished yet . +* Issue#38 discussion - Add an “Area” data-type into CAMARA_common.yaml + * “Area” data-type for CAMARA_common is not ready for Commnonalities now. + * NSB will refer to the "Area" data-type from device-locaction project before Commnonalities definition + * NSB will follow the update of Commnonalities about “Area” data-type for CAMARA_common. + + +* Issue#39 discussion - API BACKLOG - Dedicated Networks: Scope Enhancement proposal + * Thorsten introduced Dedicated Network API proposal, which aims to provide a highly abstract NaaS API which can support both FBB and MBB scenarios. Thorsten introded the differences between Dedicated Network API with QoD, Site To Cloud VPN, and NSB, which are included in the Proposal PDF. + * Shuting comment that it's a great proposal for long term plan. There are different ways of the slice/vpn/leased line compositions regarding on AN, TN, CN respectively. "Dedicated Networks" needs time to really support all ways of network compositions. From commercial side, it also needs to think about the product setting problem, especially when it comes to price. Eg. In terms of TN, OTN is far more expensive than IP. + * It will take some time to discuss the proposals in the Issue#39 + + +## AOB +1. The next call will be on Friday, 2nd Aug, 16:00 CST / 10:00 CET + + + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23.md new file mode 100644 index 0000000000000000000000000000000000000000..2fd235886be14f534e45a9c34c216a66df30c335 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-05-23.md @@ -0,0 +1,34 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-05-23 + + +*Friday, May 23rd, 2025* + + +## Attendees +* Dongrui Xiao (China Unicom) +* Xunli Yang (Huawei) +* Rafal Artych (DT) +* Masaharu Hattori(KDDI) + + +## Agenda +* Issue#46 discussion - prepare for the version release, update the API Yaml +* PR#20 update - API Design documentation update +* AOB + + +## Issues Discussions +* Issue#46 discussion + * Still modify the yaml file, change api version to 0.1.0-alpha.1 and prepare for the version release. + * Update the test case files. + * +* PR#20 update - API Design documentation update + * The remaining PR#20 has been discussed well. + * NSB will update the API Design documentation and continuously modify it following the Commnonalities. + + +## AOB +1. The next call will be on Friday, 6th June, 16:00 CST / 10:00 CET + + + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06.md new file mode 100644 index 0000000000000000000000000000000000000000..a02a280f751118d08d70a17665549e3441fc3241 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-06-06.md @@ -0,0 +1,39 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-06-06 + + +*Friday, June 6th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Rafal Artych (DT) +* Surajj Jaggernath (Vodafone) +* Vidhi Mehta () + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* Issue#54 discussion - prepare for the version release, update the API Yaml +* Issue#51 discussion - prepare API test cases +* AOB + + +## Issues Discussions +* Issue#54 discussion - prepare for the version release, update the API Yaml + * Some error code has been refined, and discuss the description. + * Modify the yaml file, Remove 401 AUTHENTICATION_REQUIRED error code according to camaraproject/Commonalities#429. + * +* Issue#51 discussion - prepare API test cases + * Modify API test cases based on yaml changes. + +## Timeline +* Need to follow up with CAMARA release management. +* Pre-release with API release candidate version need to prepared and released +* Create release PR for delivering the release version r1.1 for Fall25 M3 milestone -June 21st + +## AOB +1. The next call will be on Friday, 20th June, 16:00 CST / 10:00 CET + + + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04.md new file mode 100644 index 0000000000000000000000000000000000000000..993a5b88d36ba667dbfae4323879d86e87bd6b9a --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-04.md @@ -0,0 +1,41 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-07-04 + + +*Friday, July 4th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Rafal Artych (DT) +* Masaharu Hattori (KDDI) +* Veerat Kulkarni + + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* PR#59 discussion - add some developer-friendly API description, make some general terminology adjustments. +* Free discussion +* AOB + + +## Issues Discussions +* PR#59 discussion + * Add some developer-friendly API description in yaml file. + * Unified the terminology for the defined QoSProfile parameters to align with QoD. + * Ready for the API release-candidate version. +* Free discussion - Business Model for Sclice Booking + * If there is a new infrastructure needs to be spawned up for the specific network slice booking instance, what is the price model for the specific slice? + * Action: This issue can be further discussed in detail after the meeting through email or issue channels. + +## Timeline +* Need to follow up with CAMARA release management. +* Merge PR#54, and release API release candidate version r1.1. + +## AOB +1. The next call will be on Friday, 18th July, 16:00 CST / 10:00 CET + + + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18.md new file mode 100644 index 0000000000000000000000000000000000000000..0a5182efe5a9fa2ef7cd3920f646283218522a0d --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-07-18.md @@ -0,0 +1,50 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-07-18 + + +*Friday, July 18th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Masaharu Hattori (KDDI) +* Surajj Jaggernath (Vodafone) + + + + +## Agenda +* Introduce the current progress of API Release and the next plan +* Issue#63 discussion - Naming pattern correction. +* Issue#64 discussion - Supplemental description fields for the API endpoints. +* Issue#65 discussion - Modify the name for schema QosProfile to avoid confusions. +* Free discussion +* AOB + + +## Issues Discussions +* Issue#63 discussion + * Property and similar names should follow lowerCamelCase naming pattern + * Schema names follow UpperCamelCase naming pattern +* Issue#64 discussion + * Post: Add description field to help the developers understand the endpoint API better. + * Delete: Ideally this should have some explanation about delete usage e.g. what is the effect of deleting the session befor the endtime that is was booked for, etc. + * Get: The description may contain more details about the provided resource information that is returned when calling this end-point. +* Issue#65 discussion +* Modify the name for schema QosProfile to avoid confusions. + * There is already a definition for QosProfile within the API qos-profiles in QualityOnDemand which is different from the definition here (as defined as profile for one device). + * Consider to modify the name for the profile which is specific for NetworkSliceBooking to avoid confusions. + * Action: decided on the name `SliceQosProfile`. +* Free discussion + * The plan for the API of managing device access. + * Plan to release this part of API in the next release(Spring26). + +## Timeline +* Need to follow up with CAMARA release management. +* Merge PR#54, and release API release candidate version r1.1. + +## AOB +1. The next call will be on Friday, 1st Aug, 16:00 CST / 10:00 CET + + + diff --git a/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26.md b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26.md new file mode 100644 index 0000000000000000000000000000000000000000..a05359b3f87f9c2d5f854d7b1f5f8094ffedb1f6 --- /dev/null +++ b/original/NetworkSliceBooking/documentation/MeetingMinutes/MOM-2025-09-26.md @@ -0,0 +1,46 @@ +# CAMARA Network Slice Booking Meeting - MOM-2025-09-26 + + +*Friday, Sep 26th, 2025* + + +## Attendees +* Xunli Yang (Huawei) +* Xiao Dongrui (China Unicom) +* Rafal Artych (DT) + + +## Agenda +* The API is about to be released(Thanks for everyone's great work!) +* Discuss the plan for the next version in Spring26: + * Issue#81 discussion - [Generic422 error rename to be more explicit](https://github.com/camaraproject/NetworkSliceBooking/issues/81). + * Issue#82 discussion - [Add tests for polygon area validation limits (between 3-15 points)](https://github.com/camaraproject/NetworkSliceBooking/issues/82). + * Issue#83 discussion - [Add corresponding tests on x-correlator parameters](https://github.com/camaraproject/NetworkSliceBooking/issues/83). + * Issue#84 discussion - [Add asynchronous callback in the createSession operation](https://github.com/camaraproject/NetworkSliceBooking/issues/84). +* Free discussion +* AOB + + +## Issues Discussions +* Meta-release Fall25 + * Network-slice-booking v0.1.0 is about to be released in Fall25. + * Keep an eye on the possible release schedule for future versions, ref:[Proposal to Adopt a Dual-Phase Meta-Release Cadence for CAMARA APIs #194](https://github.com/camaraproject/Governance/issues/194) +* Issue#81 discussion + * Split the 422 error with "service area is not supported" error and "resources are insufficient" error. + * Optional change: + * `NetworkSliceBooking422` -> `SERVICEAREA_NOT_SUPPORTED` for "service area is not supported" error. + * `NetworkSliceBooking422` -> `RESOURCES_INSUFFICIENT` for "resources are insufficient" error. +* Issue#82 discussion + * Add tests for polygon area validation limits (between 3-15 points). +* Issue#83 discussion + * Add corresponding tests on x-correlator parameters + * To be clarified: whether to add schenarios for inconsistent x-correlator in request and response. +* Issue#84 discussion + * Plan to add asynchronous callback in the next release. + * To be discussed: notification API. +* Free discussion + * Plan to release this part of API in the next release(Spring26). + + +## AOB +1. The next call will be on Friday, 10th Oct, 16:00 CST / 10:00 CET diff --git a/original/NumberRecycling/README.md b/original/NumberRecycling/README.md new file mode 100644 index 0000000000000000000000000000000000000000..d106ce40b1262b361bd77d72bba82cc4736dbf1b --- /dev/null +++ b/original/NumberRecycling/README.md @@ -0,0 +1,51 @@ + + + + + + + + + +# NumberRecycling + +Sandbox API Repository to describe, develop, document, and test the NumberRecycling API within the [Know Your Customer (KYC)](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ggCaBQ) + +## Scope + +* Service API “NumberRecycling” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the API consumer with the ability to: + * Check whether the subscriber of the phone number has changed. A common scenario is when Application service provider (ASP) wants to check whether there has been a change in the user associated with the phone number after the specified date. This allows the ASP to ensure that a phone number is correctly linked to an user and prevent the mis-delivery of SMS messages. +* Describe, develop, document, and test the API +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/NumberRecycling/releases/tag/r2.2) (Fall25), with the following API versions: + * **number-recycling v0.2.0** + [[YAML]](https://github.com/camaraproject/NumberRecycling/blob/r2.2/code/API_definitions/number-recycling.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NumberRecycling/r2.2/code/API_definitions/number-recycling.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NumberRecycling/r2.2/code/API_definitions/number-recycling.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NumberRecycling/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NumberRecycling/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NumberRecycling/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of KnowYourCustomer Sub Project are held virtually + * Schedule: Bi-weekly, Tuesday, 08:00 UTC (09:00 CET, 10:00 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Minutes: Access [meeting minutes](https://github.com/camaraproject/KnowYourCustomer/tree/main/documentation/MeetingMinutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/NumberRecycling/code/API_definitions/number-recycling.yaml b/original/NumberRecycling/code/API_definitions/number-recycling.yaml new file mode 100644 index 0000000000000000000000000000000000000000..dbb320041ffd7d8e4bc1daac19fda281427b56a1 --- /dev/null +++ b/original/NumberRecycling/code/API_definitions/number-recycling.yaml @@ -0,0 +1,351 @@ +openapi: 3.0.3 +info: + title: Number Recycling + description: | + The API can be used to check whether the subscriber of the phone number has changed. + A common scenario is when Application service provider (ASP) wants to check whether there has been a change in the user associated with the phone number after the specified date. This allows the ASP to ensure that a phone number is correctly linked to an user and prevent the mis-delivery of SMS messages. + + For example, below is a potential scenarios: + * Scenario 1 + * Pre-conditions + * User A signed a contract with MNO A for the phone number '+123456789' on October 9, 2023, and is still using it. + * User A also signed contracts with ASP A on December 22, 2023 for its services. + * ASP A holds the contract date (2023-12-22) and the phone number (+123456789) for User A. + * Currently, on November 2, 2024, ASP A wishes to send a SMS message to User A. + * Potential operations + * ASP A sends a request with specified date (2023-12-22) and phone number (+123456789) to the Number Recycling API. + * The API response sets to 'false', indicating that there has not been a change in the user associated with the phone number. + * Post-conditions + * ASP A decides to send the SMS message to User A. + * By following these steps, ASP A ensures that a phone number is linked to User A. + + Number_Recycling_scenario_1 + + Note: + * When API receives a request with specified date on which a user signed a contract with MNO, the API respond sets to 'false'(e.g., 2023-10-09 in the Scenario 1 of the figure above). + + * Scenario 2 + * Pre-conditions + * User A signed a contract with MNO A for the phone number '+123456789' on October 9, 2023, and canceled it on February 25, 2024. Subsequently, User B signed a contract with MNO A for the same phone number on September 21, 2024, and is still using it. + * User A also signed contracts with ASP A on December 22, 2023 for its services. + * ASP A holds the contract date (2023-12-22) and the phone number (+123456789) for User A. + * Currently, on November 2, 2024, ASP A wishes to send a SMS message to User A. + * Potential operations + * ASP A sends a request with specified date (2023-12-22) and phone number (+123456789) to the Number Recycling API. + * The API response sets to 'true', indicating that there has been a change in the user associated with the phone number. + * Post-conditions + * ASP A decides to stop sending the SMS message to User A and contacts User A by mail. + * By following these steps, ASP A ensures that a phone number is not linked to User A and prevents the mis-delivery of the SMS message. + + Number_Recycling_scenario_2 + + Note: + * When the API receives a request with specified date during which there is no contract with MNO for the phone number, the API respond sets to 'true'(e.g., the period between 2024-02-25 and 2024-09-20 in the Scenario 2 of the figure above). + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: tbd + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/NumberRecycling +servers: + - url: '{apiRoot}/number-recycling/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /check: + post: + security: + - openId: + - number-recycling:check + tags: + - Check Number Recycling + summary: Check whether the subscriber of the phone number has changed. + description: Check whether the subscriber of the phone number has changed. + operationId: checkNumberRecycling + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Check whether the subscriber of the phone number has changed. + content: + application/json: + schema: + $ref: '#/components/schemas/CreateCheckNumRecycling' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CheckNumRecyclingInfo" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/Generic422' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + CreateCheckNumRecycling: + type: object + required: + - specifiedDate + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + specifiedDate: + type: string + format: date + description: Specified date to check whether there has been a change in the subscriber associated with the specific phone number, in RFC 3339 calendar date format (YYYY-MM-DD). + example: "2024-10-31" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + CheckNumRecyclingInfo: + type: object + required: + - phoneNumberRecycled + properties: + phoneNumberRecycled: + type: boolean + description: | + Set to true (Boolean, not string) when there has been a change in the subscriber associated with the specific phone number after “specifiedDate”. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + responses: + Generic200: + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/CheckNumRecyclingInfo' + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + InvalidArgument: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + OutOfRange: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + Unauthenticated: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + Permission Denied: + description: Permission denied. OAuth2 token access not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + Phone Number Used By Different Network Operator: + description: Provided phone number is used by a different network operator + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Phone number not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + Device Not Applicable: + description: Service not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided phone number + Unnecessary Identifier: + description: An explicit identifier is provided when a phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the access token + Missing Identifier: + description: An identifier is not included in the request and the phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified diff --git a/original/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story.md b/original/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..e0650beaf0c2a160682a7683bdfdfafdc256dce3 --- /dev/null +++ b/original/NumberRecycling/documentation/API_documentation/Number_Recycling_User_Story.md @@ -0,0 +1,11 @@ +# Number Recycling API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check whether there has been a change in the user associated with the phone number after the specified date so that I can ensure that a phone number is correctly linked to an user and prevent mis-delivery before sending SMS messages to an user. | +| ***Roles, Actors and Scope*** | **Actors:** Application service providers (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Communication service Provider (CSP), Channel Partner.
                                                    **Scope:** Checks whether there has been a change in the user associated with the specific phone number after the specified date. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                    1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform optionally through a Channel Partner.
                                                    2. The ASP:BusinessManager has successfully subscribed to the Number Recycling API product from the product catalog optionally through a Channel Partner.
                                                    3. The ASP:Administrator has onboarded the ASP:User to the platform.| +| ***Activities/Steps*** | **Starts when:** The ASP application makes a POST request to the Number Recycling API, including specified date and the phone number provided by the user in the ASP:User. This request could be done via (or not) the Channel Partner.
                                                      **Ends when:** The CSP's Number Recycling Server responds to confirm if the user associated with the phone number has changed since the specified date. | +| ***Post-conditions*** | The ASP:User could continue offering to send the SMS messages to the user associated with the phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Recycling API operations.
                                                      - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                                      - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| diff --git a/original/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist.md b/original/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..7ee476f6184619c9e451bdf268854d5edcc28d33 --- /dev/null +++ b/original/NumberRecycling/documentation/API_documentation/number-recycling-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for number-recycling v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                      public | stable
                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/number-recycling.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/Number_Recycling_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/number-recycling.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/0AFmBQ) | diff --git a/original/NumberRecycling/documentation/SupportingDocuments/README.MD b/original/NumberRecycling/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/NumberRecycling/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/NumberVerification/README.md b/original/NumberVerification/README.md new file mode 100644 index 0000000000000000000000000000000000000000..d9938c81f25d6a001a33a1d05562a6e27414e606 --- /dev/null +++ b/original/NumberVerification/README.md @@ -0,0 +1,55 @@ + + + + + + + + + +# NumberVerification + +Incubating API Repository to evolve and maintain the definitions and documentation of the NumberVerification Service API within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XzTe) + +## Scope + +* Service API for “NumberVerification” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * verify the phone number associated with the SIM used in the device connected to the mobile data network. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 +* Incubating stage since: February 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/NumberVerification/releases/tag/r3.2) (Fall25), with the following API versions: + * **number-verification v2.1.0** + [[YAML]](https://github.com/camaraproject/NumberVerification/blob/r3.2/code/API_definitions/number-verification.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/NumberVerification/r3.2/code/API_definitions/number-verification.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/NumberVerification/r3.2/code/API_definitions/number-verification.yaml) +* The latest public release is always available here: https://github.com/camaraproject/NumberVerification/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/NumberVerification/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/NumberVerification/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564484/Minutes+-+Number+Insights) +* Mailing list: + * To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . + * A message to all Contributors of this Sub Project can be sent using . +* [Slack channel](https://app.slack.com/client/T05S5J43YQP/C062DDGR60L) diff --git a/original/NumberVerification/code/API_definitions/number-verification.yaml b/original/NumberVerification/code/API_definitions/number-verification.yaml new file mode 100644 index 0000000000000000000000000000000000000000..372d3db17611be386ff473586f7b843c996897bf --- /dev/null +++ b/original/NumberVerification/code/API_definitions/number-verification.yaml @@ -0,0 +1,320 @@ +openapi: 3.0.3 +info: + title: Number Verification + description: | + This API can verify or retrieve the **mobile phone number** that is currently allocated by the network operator to the SIM in the end user's device + + In this API **phone number** refers to the mobile phone number. + + # Introduction + + The Number Verification API is used by the API consumer to perform real-time checks to verify the phone number of a mobile device being used to access the application. This check can be done either by the API provider, returning "true" or "false", or by the application, by matching the phone number returned by the API Provider with the phone number of the device that is being used. + + It uses silent authentication (Network-based authentication or SIM-Based authentication) to verify possession of a phone number in the background without requiring user interaction. There are neither one-time passwords (OTP) received by SMS nor authenticator app downloads, so it is much simpler. It can be used at sign up, login, or transaction time to validate that a user's SIM is not spoofed or cloned. + + # Relevant Definitions and Concepts + + - **Network-Based Authentication**: Authentication mechanism based on the identification of the mobile phone. + A network operator knows to which subscriber a connected mobile phone belongs and what its associated phone number is. + - **SIM-Based Authentication**: Authentication mechanism based on the identification of the subscriber's SIM installed in the user's device. This mechanism relies on temporary tokens provided by the operator, as defined by [GSMA TS.43](https://www.gsma.com/newsroom/gsma_resources/ts-43-service-entitlement-configuration/) and [GSMA ASAC](https://www.gsma.com/newsroom/gsma_resources/asac-01-v1-0/). + + # API Functionality + + This API enables an API Consumer to verify or retrieve the phone number of the mobile device being used to access their service. + + # The Authentication Request + + **For NumberVerification the API provider guarantees that there is no user interaction.** Would user interaction be needed the authorization server returns an error. + Authentication methods such as SMS OTP or user/password are incompatible, as the goal is to validate the mobile phone number that is accessing the App. + + ## Authentication Request with a temporary token + + If the API Consumer has a TS.43 temporary token created on the mobile device then this API works over all connections e.g. WiFi taking advantage of the SIM-Based authentication. + The API Consumer sends the temporary token to their backend which either: + - Sends a CIBA Authentication Request, as described in the current release [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement), with a parameter `login_hint=operatortoken:`. + - Or sends a JWT-Bearer token request as described in [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement), with the TS.43 token in the `sub` claim of the JWT assertion with the format `"operatortoken:"`. + + How the API Consumers get a TS.43 temporary token and how this token is sent to their backend, is out-of-scope of the API definition. + + ## Authentication Request without a temporary token + + If the API Consumer does not have a TS.43 temporary token then the API Consumer must use OpenId Connect Authorization Code Flow as described in the current release of [CAMARA APIs Access and User Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement). + For this method of authentication to work, the device must be connected to the mobile network. + + The API Consumer should use the request parameter prompt=none in the Authentication Request, as described in **[OIDC Connect](https://openid.net/specs/openid-connect-core-1_0.html#AuthRequest)**, ensuring no user interaction. + The API Provider implies the request parameter prompt=none in the Authentication Request for this API. + + # Resources and Operations overview + + This API currently provides two endpoints which both require a **3-legged token** obtained by using one of the two methods indicated in _The Authentication Request_ section. This therefore **excludes** using, for example, SMS/OTP or user/password as an authentication method: + - The /verify endpoint checks whether the mobile phone number registered by the user with the API consumer matches the one actually associated with the mobile device. + It can receive either a hashed or a plain text phone number as input. + It compares the received phone number with the user's phone number associated to the access token in order to respond **true/false**. + - The /device-phone-number endpoint returns the phone number associated by the network operator with the SIM in the end user's device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to [Identity and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + In the case of the Number Verification API scenario and according to the API definition, 3-legged access tokens must be used by API clients to invoke this API with dedicated scope. The API client must authenticate on behalf of a specific user to use this service. This must be done via mobile network authentication. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/NumberVerification +servers: + - url: '{apiRoot}/number-verification/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath +tags: + - name: Phone number verify + description: API operation to verify a phone number received as input. It can be received either in plain text or hashed format. + - name: Phone number share + description: API operation to return the phone number associated to the access token. +paths: + /verify: + post: + tags: + - Phone number verify + summary: Verifies if the received hashed/plain text phone number matches the phone number associated with the access token + description: | + Verifies if the specified phone number (either in plain text or hashed format) matches the one that the user is currently using. Only one of the plain or hashed formats must be provided. + - The number verification will be done for the user that has authenticated via mobile network + - It returns true/false depending on if the hashed phone number received as input matches the authenticated user's `device phone number` associated to the access token + operationId: phoneNumberVerify + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationRequestBody' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationMatchResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/PhoneNumberVerificationPermissionDenied403' + security: + - openId: + - number-verification:verify + /device-phone-number: + get: + tags: + - Phone number share + summary: Returns the phone number associated with the access token + description: | + Returns the phone number so the API clients can verify the number themselves: + - It will be done for the user that has authenticated via mobile network + - It returns the authenticated user's `device phone number` associated to the access token + operationId: phoneNumberShare + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/NumberVerificationShareResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/PhoneNumberVerificationPermissionDenied403' + security: + - openId: + - number-verification:device-phone-number:read +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + NumberVerificationRequestBody: + type: object + description: Payload to verify the phone number. + minProperties: 1 + maxProperties: 1 + properties: + phoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + hashedPhoneNumber: + description: Hashed phone number. SHA-256 (in hexadecimal representation) of the mobile phone number in **E.164 format (starting with country code)**. Prefixed with '+'. + type: string + pattern: '^[a-fA-F0-9]{64}$' + example: 32f67ab4e4312618b09cd23ed8ce41b13e095fe52b73b2e8da8ef49830e50dba + NumberVerificationMatchResponse: + type: object + description: Number verification result + required: + - devicePhoneNumberVerified + properties: + devicePhoneNumberVerified: + $ref: '#/components/schemas/DevicePhoneNumberVerified' + NumberVerificationShareResponse: + type: object + description: Number verification share result + required: + - devicePhoneNumber + properties: + devicePhoneNumber: + $ref: '#/components/schemas/DevicePhoneNumber' + DevicePhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + DevicePhoneNumberVerified: + description: Number verification. True, if it matches + type: boolean + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + example: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + PhoneNumberVerificationPermissionDenied403: + description: | + Client does not have sufficient permission. + In addition to regular scenario of `PERMISSION_DENIED`, other scenarios may exist: + - Client authentication was not via mobile network. In order to check the authentication method, AMR parameter value in the 3-legged user's access token can be used and make sure that the authentication was not either by SMS+OTP nor username/password (`{"code": "NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK","message": "Client must authenticate via the mobile network to use this service"}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK: + value: + status: 403 + code: NUMBER_VERIFICATION.USER_NOT_AUTHENTICATED_BY_MOBILE_NETWORK + message: Client must authenticate via the mobile network to use this service diff --git a/original/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md b/original/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..6ecb3f65f092760d73b12df55469e38924798542 --- /dev/null +++ b/original/NumberVerification/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md @@ -0,0 +1,10 @@ +# Number Verification Share Device Phone Number API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want to retrieve the phone number associated with a mobile connection from which the API call was made, so that I can ensure that I obtain the correct phone number and avoid fraud e.g. identity theft. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                      **Scope:**
                                                      -Returns the phone number associated with the access token so the ASPs can get the phone number and verify it themselves.| +| ***Pre-conditions*** |The preconditions are listed below:
                                                      1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                      2. The ASP:BusinessManager has successfully subscribed to the Number Verification product from the CSP's product catalog via (or not) a Channel Partner.
                                                      3. The ASP:Administrator has onboarded the ASP:User to the CSP API platform via (or not) a Channel Partner.
                                                      4. The ASP:User performs an authorization request to CSP.
                                                      5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                      6. The ASP:User get the access token, via (or not) the Channel Partner, based on network authentication to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the number verification API. This request could be done via (or not) the Channel Partner.
                                                        **Ends when:** The CSP's Number Verification Server answers providing the phone number corresponding to the one of the end-user's device from which the request was triggered. The ASP:User can check if this number corresponds to the one keyed by the End-User. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the End-User phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Verification API operations
                                                        - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                        - Not able to provide: Client authentication was not performed via mobile network or temporary token. Not working on mobile hotspot (tethering) neither Wifi nor VPN mobile connections **if client authentication is performed via mobile network** | \ No newline at end of file diff --git a/original/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story.md b/original/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..3ed20b3c0a7619c1188091c4f17b90ac6a227afb --- /dev/null +++ b/original/NumberVerification/documentation/API_documentation/NumberVerification_verify_User_Story.md @@ -0,0 +1,10 @@ +# Number Verification Verify API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I want to verify the phone number associated with a mobile connection so I can validate the phone number identity that a end-user introduces in my application during a registration process.| +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                        **Scope:**
                                                        - Verifies if the specified phone number (plain text or hashed format) matches the one that the user is currently using. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                        1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                        2. The ASP:BusinessManager has successfully subscribed to the Number Verification product from the CSP's product catalog via (or not) a Channel Partner.
                                                        3. The ASP:Administrator has onboarded the ASP:User to the CSP API platform via (or not) a Channel Partner.
                                                        4. The ASP:User performs an authorization request to CSP.
                                                        5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                        6. The ASP:User get the access token, via (or not) the Channel Partner, based on network authentication to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the number verification API providing in the request the phone number provided by the End-User on the ASP:User. This request could be done via (or not) the Channel Partner. This input could be hashed or plain.
                                                          **Ends when:** The CSP's Number Verification Server responds to confirm whether the provided phone number matches the end-user's device from which the request was initiated or not. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the user phone number. | +| ***Exceptions*** | Several exceptions might occur during the Number Verification API operations
                                                          - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                          - Invalid input: Not valid input data to invoke operation (e.g. phone number without the '+' prefix).
                                                          - Not able to provide: Client authentication was not performed via mobile network or temporary token. Not working on mobile hotspot (tethering) neither Wifi nor VPN mobile connections **if client authentication is performed via mobile network** | \ No newline at end of file diff --git a/original/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist.md b/original/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..2e17cea936ec22a7aa8da4b076d17a7255078f99 --- /dev/null +++ b/original/NumberVerification/documentation/API_documentation/number-verification-API-Readiness-Checklist.md @@ -0,0 +1,32 @@ +# API Readiness Checklist + +Checklist for number-verification v2.1.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | public-release
                                                          initial | public-release
                                                          stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/number-verification.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/number-verification.yaml) | +| 6 | User stories | O | O | O | M | Y | [get](/documentation/API_documentation/NumberVerification_device_phone_number_User_Story.md) [verify](/documentation/API_documentation/NumberVerification_verify_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [get](/code/Test_definitions/number-verification-phoneNumberShare.feature) [verify](/code/Test_definitions/number-verification-phoneNumberVerify.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [get](/code/Test_definitions/number-verification-phoneNumberShare.feature) [verify](/code/Test_definitions/number-verification-phoneNumberVerify.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue[#216](https://github.com/camaraproject/NumberVerification/issues/216) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | Y | [link](https://www.open-gateway.com/operators-map) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81134263/NumberVerification+API+description) | + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + diff --git a/original/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..c287b83356ba212a848b7d7507652e60ee7f1e55 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2022_Week46_syncCalls.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/original/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..aeb6a9ad18abfb8feb29b6b1dc349567fbb905ab --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2022_Week50_syncCalls.md @@ -0,0 +1,101 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >discussion continued on Thursday 15th Dec'22 + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                                                          Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                                                          + +### NumberVerify + +#### Recommendation: + + >Enable Number Verify API with two flavors: + - Based on dedicated endpoint (Orange + TEF proposal) + - Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design. +In the second case, this particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - work with 2 yaml files with API description. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4c4a7282f9bb1db14f8a46ff35be6f948d9369ef --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week14_syncCalls.md @@ -0,0 +1,49 @@ +# Week 14 meeting + +## Participants + +4th April 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|JORGE GARCIA HOSPITAL|Telefonica| +|5|PEDRO ANTONIO DE ALARCON SANCHEZ|Telefonica| +|6|Ludovic ROBERT|Orange| +|7|Cormac Hegarty|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- [Issue #16](https://github.com/camaraproject/SimSwap/issues/16) +- participants discussed a scenario, when Service Provider requests sim swap information from MNO, but MNO has not registered an event of a sim Change. MNO performed API service, but value cannot be returned. Success (200OK) or Error (401 or 404) has implications for API consumer. We continue discusson to find a solution that can be described in API documentation. +- + +### NumberVerify + +- [Issue #35](https://github.com/camaraproject/NumberVerification/issues/35) +- participants identified that current API descriptions might be confusing for software developers - two API definitions: MobileConnect & Camara flavors +- Mobile Identity APIs are commercially available and software developers are familiar with existing API design - making a change to existing standard might not be identified by software developers community as a positive change, due to existing Mobile Connect implementations +- additionally, recent changes inside commonalities working group describing the [notation of APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md#42-inputoutput-resource-definition), requires adoption of Mobile Connect API definition to be compliant with CAMARA +- there is a willingness to assess benefits developers can get when having APIs fully compliant to MC but not same from one implementation to another . + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion on next alignment call that takes place 13th April 2023. diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4639992f7412b80dbb4481c6e0866f1977c2e961 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week20_syncCalls.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4bc16d0e1e7c45a108ac368ad066ec354b9d5266 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week22_syncCalls.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..781b58c433f89b8f85172128ff1fe8160a66058f --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week24_syncCalls.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..29f94863f6102e0436cc97e3758804e9de8c7bc5 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week26_syncCalls.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..bfcff40a9b4d184e1e31063cec0dd15c5625b4fe --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week2_syncCalls.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delivered + +### NumberVerify + +- CAMARA & MC APIs yaml files delivered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..dbaf949d9342dc586b323020dd24d58af93a054c --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week32_syncCalls.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71e4117b347508f92e11b975698fad270626d34e --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week36_syncCalls.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ef5342ee522e0fba8d0eb487ef07eabb7eeb0dec --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week38_syncCalls.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..1857dd5413eee798ae40bb821395fd5f077994ad --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week40_syncCalls.md @@ -0,0 +1,65 @@ +# Week 40 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71b83502cdd314d2723ed46f852e4e1e6cad899b --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2023_Week42_syncCalls.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..2e87b4b18e751b1dfca19d0ccbff58516a21703b --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week10_syncCalls.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4d21478b982bd60ae559d9aa4e6398cf0949b7ff --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week12_syncCalls.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..0d3113d9a121a5cfefa735d20a647e062a863fc2 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week2_syncCalls.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..8231efe5770b6d7f1e29a80710342d8b0f24bf64 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week4_syncCalls.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..1adedb2e915a338bdc3bc4a46fb783bf228fd43b --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week6_syncCalls.md @@ -0,0 +1,42 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB + +* discussion about MWC 2024 +* add commits to sub-projects for next release + +## APs diff --git a/original/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls.md b/original/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..04cbf65fda5ec2212f67cc70bf17681e3866c51a --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/2024_Week8_syncCalls.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/original/NumberVerification/documentation/MeetingMinutes/README.MD b/original/NumberVerification/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..c1a309ed5daa4dc11a59644c59c98df70c9d35e4 --- /dev/null +++ b/original/NumberVerification/documentation/MeetingMinutes/README.MD @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [Number Verification Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/NumberVerification) diff --git a/original/OTPValidation/README.md b/original/OTPValidation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..b251a3ce4f0f69b81750b85c000f636f9127d6d0 --- /dev/null +++ b/original/OTPValidation/README.md @@ -0,0 +1,64 @@ + + + + + + + + + +# OTPValidation + +Incubating API Repository to evolve and maintain the definitions and documentation of OTPValidation Service API within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/yDXe) + +## Scope + +* Service APIs for “OTPValidation” (see APIBacklog.md) + * The OTP SMS API facilitates real-time verification of a user's device by sending a unique code via SMS to the specified mobile phone number. The process involves three key steps: +1. **Code Generation and Delivery:** + The send-code operation is used by the API consumer (e.g., an application) to request a one-time code to be sent by SMS to the application user's mobile phone along with an message to the user's mobile device. +2. **User Input:** + The user receives the SMS and enters the received code into the application. +3. **Verification:** + The application submits the entered code using the validate-code operation, which then verifies its accuracy and responds with a confirmation indicating whether the code is valid. + +This process ensures secure, real-time validation of user possession of the specified device, enhancing authentication security. + * by delivering a one-time password (OTP) to it through SMS and validating the received code with the user's operator after the code is entered as requested. + * Started: October 2022 + * Incubating stage since: February 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/OTPValidation/releases/tag/r3.2) (Fall25), with the following API versions: + * **one-time-password-sms v1.1.1** + [[YAML]](https://github.com/camaraproject/OTPValidation/blob/r3.2/code/API_definitions/one-time-password-sms.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/OTPValidation/r3.2/code/API_definitions/one-time-password-sms.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/OTPValidation/r3.2/code/API_definitions/one-time-password-sms.yaml) +* The latest public release is always available here: https://github.com/camaraproject/OTPValidation/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/OTPValidation/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/OTPValidation/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564484/Minutes+-+Number+Insights) +* Mailing list + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . + + + diff --git a/original/OTPValidation/code/API_definitions/one-time-password-sms.yaml b/original/OTPValidation/code/API_definitions/one-time-password-sms.yaml new file mode 100644 index 0000000000000000000000000000000000000000..cf250afb055ea40593980eefaee4661c59b9a3ae --- /dev/null +++ b/original/OTPValidation/code/API_definitions/one-time-password-sms.yaml @@ -0,0 +1,445 @@ +openapi: 3.0.3 +info: + title: One Time Password SMS + description: |- + Service API to send short-lived OTPs (one time passwords) to a phone number via SMS and validate it afterwards, in order to verify the phone number as a proof of possession. + + # Relevant Definitions and concepts + - **OTP**: *One Time password* is a one-time authorization code that is valid for only one login session or transaction. + + # API Functionality + It enables a Service Provider (SP) to send an OTP code by SMS and validate it to verify the phone number (MSISDN) as a proof of possession. + + # Resources and Operations overview + This API currently provides two endpoints, one to send an OTP to a given phone number and another to validate the code received as input. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/OTPValidation +servers: + - url: "{apiRoot}/one-time-password-sms/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: OTP Management + description: API operations to manage OTP codes +paths: + /send-code: + post: + tags: + - OTP Management + summary: Sends a message including an OTP code to the given phone number + description: |- + Sends an SMS with the desired message and an OTP code to the received phone number. + operationId: sendCode + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/SendCodeBody' + required: true + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/SendCodeResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/SendCodeForbiddenError403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - one-time-password-sms:send-validate + /validate-code: + post: + tags: + - OTP Management + summary: Verifies the OTP received as input + description: |- + Verifies the code is valid for the received authenticationId + operationId: validateCode + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/ValidateCodeBody' + required: true + responses: + '204': + description: The OTP was successfully validated + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/ValidateCodeBadRequestError400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - one-time-password-sms:send-validate +components: + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SendCodeBody: + description: Structure to request sending a code to a phone number + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + message: + $ref: '#/components/schemas/Message' + required: + - message + - phoneNumber + SendCodeResponse: + description: Structure to provide authentication identifier + type: object + properties: + authenticationId: + $ref: '#/components/schemas/AuthenticationId' + required: + - authenticationId + ValidateCodeBody: + description: Strcuture to request code verification + type: object + properties: + authenticationId: + $ref: '#/components/schemas/AuthenticationId' + code: + $ref: '#/components/schemas/Code' + required: + - authenticationId + - code + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+346661113334' + Message: + type: string + description: Message template used to compose the content of the SMS sent to the phone number. It must include the following label indicating where to include the short code `{{code}}` + pattern: .*\{\{code\}\}.* + maxLength: 160 + example: '{{code}} is your short code to authenticate with Cool App via SMS' + AuthenticationId: + type: string + description: unique id of the verification attempt the code belongs to. + maxLength: 36 + example: ea0840f3-3663-4149-bd10-c7c6b8912105 + Code: + type: string + description: temporal, short code to be validated + maxLength: 10 + example: AJY3 + ErrorInfo: + description: Structure to describe error + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + ValidateCodeBadRequestError400: + description: |- + Problem with the client request. In addition to regular scenario of `INVALID_ARGUMENT`, another scenarios may exist: + - Too many unsuccessful attempts (`{"code": "ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED","message": "The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP"}`) + - Expired authenticationId (`{"code": "ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED","message": "The authenticationId is no longer valid"}`) + - OTP is not valid for the provided authenticationId (`{"code": "ONE_TIME_PASSWORD_SMS.INVALID_OTP","message": "The provided OTP is not valid for this authenticationId"}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED + - ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED + - ONE_TIME_PASSWORD_SMS.INVALID_OTP + examples: + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param + OTP_VALIDATION_400_VERIFICATION_FAILED: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED + message: The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP + OTP_VALIDATION_400_VERIFICATION_EXPIRED: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED + message: The authenticationId is no longer valid + OTP_VALIDATION_400_INVALID_OTP: + value: + status: 400 + code: ONE_TIME_PASSWORD_SMS.INVALID_OTP + message: The provided OTP is not valid for this authenticationId + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SendCodeForbiddenError403: + description: |- + Client does not have sufficient permissions to perform this action. + In addition to regular scenario of `PERMISSION_DENIED`, another scenarios may exist: + - Too many code requests were sent (`{"code": "ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED","message": "Too many OTPs have been requested for this MSISDN. Try later."}`) + - The given phoneNumber can't receive an SMS due to business reasons in the operator, e.g. fraud, receiving SMS is not supported, etc (`{"code": "ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED","message": "Phone_number can't receive an SMS due to business reasons in the operator."}`) + - The given phoneNumber is blocked to receive SMS due to any blocking business reason in the operator (`{"code": "ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED","message": "Phone_number is blocked to receive SMS due to any blocking business reason in the operator."}`) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED + - ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED + - ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED + examples: + GENERIC_403_PERMISSION_DENIED: + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action + OTP_VALIDATION_403_MAX_OTP_CODES_EXCEEDED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED + message: Too many OTPs have been requested for this MSISDN. Try later. + OTP_VALIDATION_403_PHONE_NUMBER_NOT_ALLOWED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED + message: Phone_number can't receive an SMS due to business reasons in the operator. + OTP_VALIDATION_403_PHONE_NUMBER_BLOCKED: + value: + status: 403 + code: ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED + message: Phone_number is blocked to receive SMS due to any blocking business reason in the operator. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic429: + description: Either out of resource quota or reaching rate limiting + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. diff --git a/original/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story.md b/original/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..272a0890bad7550da6c033a1896e97f9cdc4d71c --- /dev/null +++ b/original/OTPValidation/documentation/API_documentation/OTPValidationAPI_User_Story.md @@ -0,0 +1,27 @@ +# OTPVAlidationAPI API User Story + +OTP Validation user story is splitted in 2 steps. Both steps are mandatory to perform this user story. + + +## Step 1 - Request to send a code + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the phone number associated with the line from which the call was made, so I can get a proof of possession of the phone number. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User, Customer:BusinessManager, Customer:Administrator
                                                          **Actors:** Application service providers, hyperscalers, application developers, end users, Communication service Provider (CSP).
                                                          **Scope:**
                                                          - Customer:User asks CSP to send a message featuring a 'code' variable via SMS. The message is specified by Customer:User. In the API response a request identifier is provided to link with validation step. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                          1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                          2. The Customer:BusinessManager has successfully subscribed to the OTP Validation API product from the product catalog.
                                                          3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                          4. The Customer:User performs an authorization request to CSP
                                                          5. The Customer:user has the access token allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The customer application makes a POST send-code via the OTPValidation API providing in the request the phone number keyed by the user on the application and a message to be displayed in the SMS. This message must indicate where the code must be indicated (like _"Your code to validate your onboarding for niceApp is {code}"_).
                                                            **Ends when:** The CSP OTP Validation server performs two operations: 1/answers to the API request providing a request identifier (authenticationId), and 2/send the SMS to the line identified by provided phone number. | +| ***Post-conditions*** | The customer application has a request identifier (authenticationId) and will be able to validate code keyed by the end user. | +| ***Exceptions*** | Several exceptions might occur during the OTP Validation API operations
                                                            - Unauthorized: Not valid credentials.
                                                            - Invalid input: Not valid input data to invoke operation (e.g. phone number without the '+' prefix).
                                                            - Permission denied: Too any request to send code for a phone number in a short time.
                                                            - Permission denied: phone number not able to receive SMS.| + + +## Step 2 - Validate a code + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the phone number associated with the line from which the call was made, so I can get a proof of possession of the phone number. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User, Customer:BusinessManager, Customer:Administrator
                                                            **Actors:** Application service providers, hyperscalers, application developers, end users, Communication service Provider (CSP).
                                                            **Scope:**
                                                            - Following a send code request, Customer:User asks end user to keyed the code received by SMS. Then Customer:User sends this code to the CSP to validate that the code matches the one send by the CSP in the SMS. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                            1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                            2. The Customer:BusinessManager has successfully subscribed to the OTP Validation API product from the product catalog.
                                                            3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                            4. The Customer:User performs an authorization request to CSP
                                                            5. The Customer:User has the access token allowing a secure access of the API.
                                                            6. The Customer:User has performed a valid send-code previously and has the request identifier (authenticationId).
                                                            7. The end user received via a SMS a code and keyed it on the application. | +| ***Activities/Steps*** | **Starts when:** The Customer-User makes a POST validate-code via the OTPValidation API providing in the request the code keyed by the end user on the application and the authenticationId obtained in the response of the send-code step. .
                                                              **Ends when:** The CSP OTP Validation server check the code and answers 204 if the code matches else an exception is sent. | +| ***Post-conditions*** | The customer application could continue offering its service to the end user with the confirmation of the end user phone number. | +| ***Exceptions*** | Several exceptions might occur during the OTP Validation API operations
                                                              - Unauthorized: Not valid credentials.
                                                              - Invalid input: Not valid input data to invoke operation (e.g. code not provided).
                                                              - Invalid input: The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP
                                                              - Invalid input:The provided OTP is not valid for this authenticationId
                                                              - Invalid input:The authenticationId is no longer valid| diff --git a/original/OTPValidation/documentation/API_documentation/OTP_SMS_API.md b/original/OTPValidation/documentation/API_documentation/OTP_SMS_API.md new file mode 100644 index 0000000000000000000000000000000000000000..a804e19e41981c6939b1eb963a1ab274cb65b2e8 --- /dev/null +++ b/original/OTPValidation/documentation/API_documentation/OTP_SMS_API.md @@ -0,0 +1,147 @@ +# Overview + +One Time Password SMS API is used to send short-lived OTPs (one time passwords) to a phone number via SMS and validate it afterwards, in order to provide a proof of possession of the phone number. + +## 1\. Introduction + +One Time Password SMS API performs real-time checks to verify that the user possessed the device that carries the indicated mobile phone number. It provides a frequent method of verifying possession of the device by delivering an OTP (one-time password) through SMS and validating it afterwards. + +SMS OTP (one time password) is a secure method for providing one-time access to an application or performing a single transaction. OTP is most effective and legitimate for a single transaction, unlike user-generated passwords. It is a secure authentication method where a text containing a unique alphanumeric or numeric code is sent to a mobile number (MSISDM). + +The recipient then uses this code or password as an additional layer of security to login to a service, website or app. + + +## 2\. Quick Start + +The usage of the API is based on several resources. + +Before starting to use the API, the developer needs to know about the below specified details: + +**API service endpoint** + +Two endpoints are defined in One Time Password SMS API:
                                                              +- POST /one-time-password-sms/v0/send-code : Sends an SMS with the desired message and an OTP code to the received phone number +- POST /one-time-password-sms/v0/validate-code : Verifies the received code as input is valid for the given authenticationId. + +**Authentication** + +Security access token based on two-legged authentication is required for this API with dedicated scope. + +Sample API invocations are presented in Section 4.6. + +## 3\. Authentication and Authorization + +One Time Password SMS API uses OAUTH 2.0 client credentials grant which is applicable for server to server use cases involving trusted partners or clients without any protected user data involved. [[1]](#1) + +## 4\. API Documentation + +### 4.1 API Version + +0.1.0 + +### 4.2 Details + +#### 4.2.1 Endpoint Definition + +Following table defines API endpoints of exposed REST based for One Time Password SMS API operations. + +| **Endpoint** | **Operation** | **Description** | +| -------- | --------- | ----------- | +| POST /one-time-password-sms/v0/send-code | **Request to send an OTP code** | Create request in order to send an OTP code with the given message to a mobile phone number | +| POST /one-time-password-sms/v0/validate-code | **Request to validate an OTP code** | Create a request to validate an OTP code for the given authenticationId | + + +#### One Time Password SMS API Resource Operations: +
                                                              + +| **Request code** | +| -------------------------- | +| **HTTP Request**
                                                              POST /one-time-password-sms/v0/send-code
                                                              **Query Parameters**
                                                              No query parameters are defined.
                                                              **Path Parameters**
                                                              No path parameters are defined.
                                                              **Request Body Parameters**
                                                              **phoneNumber**: A phone number belonging to the user. 'E164 with +' format.
                                                              **message**: Message template used to compose the content of the SMS sent to the phone number. It must include the following label indicating where to include the short code `{{code}}`. + +
                                                              **Response**
                                                              **200: OK**
                                                              Response body:
                                                              **authenticationId** : Unique id of the verification attempt the code belongs to.
                                                              **400:** **INVALID_ARGUMENT**
                                                              **401:** **UNAUTHENTICATED**
                                                              **403:** **PERMISSION_DENIED**
                                                              **403:** **ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED**
                                                              **403:** **ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED**
                                                              **403:** **ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED**
                                                              **404:** **NOT_FOUND**
                                                              **405:** **METHOD_NOT_ALLOWED**
                                                              **406:** **NOT_ACCEPTABLE**
                                                              **415:** **UNSUPPORTED_MEDIA_TYPE**
                                                              **429:** **TOO_MANY_REQUESTS**
                                                              **500:** **INTERNAL**
                                                              **503:** **UNAVAILABLE**
                                                              **504:** **TIMEOUT**
                                                              +
                                                              + +
                                                              + +| **Validate code** | +| -------------------------- | +| **HTTP Request**
                                                              POST /one-time-password-sms/v0/validate-code
                                                              **Query Parameters**
                                                              No query parameters are defined.
                                                              **Path Parameters**
                                                              No path parameters are defined.
                                                              **Request Body Parameters**
                                                              **authenticationId**: Unique id of the verification attempt the code belongs to.
                                                              **code**: Temporal, short code to be validated. + +
                                                              **Response**
                                                              **204: The OTP was successfully validated**
                                                              **400:** **INVALID_ARGUMENT**
                                                              **400:** **ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED**
                                                              **400:** **ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED**
                                                              **400:** **ONE_TIME_PASSWORD_SMS.INVALID_OTP**
                                                              **401:** **UNAUTHENTICATED**
                                                              **403:** **PERMISSION_DENIED**
                                                              **404:** **NOT_FOUND**
                                                              **405:** **METHOD_NOT_ALLOWED**
                                                              **406:** **NOT_ACCEPTABLE**
                                                              **415:** **UNSUPPORTED_MEDIA_TYPE**
                                                              **429:** **TOO_MANY_REQUESTS**
                                                              **500:** **INTERNAL**
                                                              **503:** **UNAVAILABLE**
                                                              **504:** **TIMEOUT**
                                                              +
                                                              + +
                                                              + +### 4.3 Errors + +Since CAMARA One Time Password SMS API is based on REST design principles and blueprints, well defined HTTP status codes and families specified by community are followed [[2]](#2). + +Details of HTTP based error/exception codes for One Time Password SMS API are described in Section 4.2 of each API REST based method. +Following table provides an overview of common error names, codes, and messages applicable to One Time Password SMS API. + +| No | Error Name | Error Code | Error Message | +| --- | ---------- | ---------- | ------------- | +|1 |400 | INVALID_ARGUMENT | "Client specified an invalid argument, request body or query param" | +|2 |400 | ONE_TIME_PASSWORD_SMS.VERIFICATION_EXPIRED | "The authenticationId is no longer valid" | +|3 |400 | ONE_TIME_PASSWORD_SMS.VERIFICATION_FAILED | "The maximum number of attempts for this authenticationId was exceeded without providing a valid OTP" | +|4 |400 | ONE_TIME_PASSWORD_SMS.INVALID_OTP | "The provided OTP is not valid for this authenticationId" | +|5 |401 | UNAUTHENTICATED | "Request not authenticated due to missing, invalid, or expired credentials" | +|6 |403 | PERMISSION_DENIED | "Client does not have sufficient permissions to perform this action" | +|7 |403 | ONE_TIME_PASSWORD_SMS.MAX_OTP_CODES_EXCEEDED | "Too many OTPs have been requested for this MSISDN. Try later." | +|8 |403 | ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_NOT_ALLOWED | "Phone_number can't receive an SMS due to business reasons in the operator" | +|9 |403 | ONE_TIME_PASSWORD_SMS.PHONE_NUMBER_BLOCKED | "Phone_number is blocked to receive SMS due to any blocking business reason in the operator" | +|10 |404 | NOT_FOUND | "A specified resource is not found" | +|11 |405 | METHOD_NOT_ALLOWED | "The requested method is not allowed/supported on the target resource" | +|12 |406 | NOT_ACCEPTABLE | "The server can't produce a response matching the content requested by the client through Accept-* headers" | +|13 |415 | UNSUPPORTED_MEDIA_TYPE | "The server refuses to accept the request because the payload format is in an unsupported format" | +|14 |429 | TOO_MANY_REQUESTS | "Either out of resource quota or reaching rate limiting" | +|15 |500 | INTERNAL | "Server error" | +|16 |503 | UNAVAILABLE | "Service unavailable" | +|17 |504 | TIMEOUT | "Request timeout exceeded. Try later." | + +
                                                              + +### 4.4 Policies + +N/A +
                                                              + +### 4.5 Code Snippets +
                                                              +Snippets elaborates REST based API call with "*curl"* to request + + +Please note, the credentials for API authentication purposes need to be adjusted based on target security system configuration. + +| Snippet 1. Request code | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/one-time-password-sms/v0/send-code`
                                                              -H 'accept: application/json'
                                                              -H 'Content-Type: application/json'
                                                              -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
                                                              -d '{ "phoneNumber": "+346661113334",
                                                              "message": "{{code}} is your short code to authenticate with Cool App via SMS"}' | +| The response will be:
                                                              200
                                                              -d '{ "authenticationId": "ea0840f3-3663-4149-bd10-c7c6b8912105" }'| +
                                                              + +| Snippet 2. Validate code | +| ----------------------------------------------- | +| curl -X 'POST' `https://sample-base-url/one-time-password-sms/v0/validate-code`
                                                              -H 'accept: application/json'
                                                              -H 'Content-Type: application/json'
                                                              -H "Authorization: Bearer eyJ0eXAiOiJKV1QiLCJhbG...."
                                                              -d '{ "authenticationId": "ea0840f3-3663-4149-bd10-c7c6b8912105",
                                                              "code": "AJY3"}' | +| The response will be:
                                                              204 | +
                                                              + + + +### 4.6 FAQs + +(FAQs will be added in a later version of the documentation) + +### 4.7 Terms + +N/A + +### 4.8 Release Notes + +N/A + + +## References + + +[1] [CAMARA Commonalities : Authentication and Authorization Concept for Service APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Working/CAMARA-AuthN-AuthZ-Concept.md)
                                                              +
                                                              [2] [HTTP Status codes spec](https://restfulapi.net/http-status-codes/)
                                                              diff --git a/original/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist.md b/original/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..a02c64d0eb6d89507a2960895f2650775bff7ba8 --- /dev/null +++ b/original/OTPValidation/documentation/API_documentation/one-time-password-sms-API-Readiness-Checklist.md @@ -0,0 +1,34 @@ +# API Readiness Checklist + +Checklist for one-time-password-sms v1.1.1 in r3.2 + + +| Nr | API release assets | alpha | release-candidate | public-release
                                                              initial | public-release
                                                              stable | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/one-time-password-sms.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v1.1.1 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/one-time-password-sms.yaml) | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/OTPValidationAPI_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [send code](/code/Test_definitions/one-time-password-sms-sendCode.feature) / [validate code](/code/Test_definitions/one-time-password-sms-validateCode.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [send code](/code/Test_definitions/one-time-password-sms-sendCode.feature) / [validate code](/code/Test_definitions/one-time-password-sms-validateCode.feature) | +| 9 | Test result statement | O | O | O | M | N | See issue [#120](https://github.com/camaraproject/OTPValidation/issues/120) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101463/OTPValidation+API+description) | + + +(1) The certified company(s) can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + + + + + + diff --git a/original/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..c287b83356ba212a848b7d7507652e60ee7f1e55 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2022_Week46_syncCalls.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/original/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..aeb6a9ad18abfb8feb29b6b1dc349567fbb905ab --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2022_Week50_syncCalls.md @@ -0,0 +1,101 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >discussion continued on Thursday 15th Dec'22 + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                                                              Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                                                              + +### NumberVerify + +#### Recommendation: + + >Enable Number Verify API with two flavors: + - Based on dedicated endpoint (Orange + TEF proposal) + - Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design. +In the second case, this particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - work with 2 yaml files with API description. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..8f6cc6a47cfb7a977498f0cdb5f6a47dc7f9109f --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week14_syncCalls.md @@ -0,0 +1,49 @@ +# Week 14 meeting + +## Participants + +4th April 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|JORGE GARCIA HOSPITAL|Telefonica| +|5|PEDRO ANTONIO DE ALARCON SANCHEZ|Telefonica| +|6|Ludovic ROBERT|Orange| +|7|Cormac Hegarty|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- [Issue #16](https://github.com/camaraproject/SimSwap/issues/16) +- participants discussed a scenario, when Service Provider requests sim swap information from MNO, but MNO has not registered an event of a sim Change. MNO performed API service, but value cannot be returned. Success (200OK) or Error (401 or 404) has implications for API consumer. We continue discusson to find a solution that can be described in API documentation. +- + +### NumberVerify + +- [Issue #35](https://github.com/camaraproject/NumberVerification/issues/35) +- participants identified that current API descriptions might be confusing for software developers - two API definitions: MobileConnect & Camara flavors +- Mobile Identity APIs are commercially available and software developers are familiar with existing API design - making a change to existing standard might not be identified by software developers community as a positive change, due to existing Mobile Connect implementations +- additionally, recent changes inside commonalities working group describing the [notation of APIs](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/API-design-guidelines.md#42-inputoutput-resource-definition), requires adoption of Mobile Connect API definition to be compliant with CAMARA +- there is a willingness to assess benefits developers can get when having APIs fully compliant to MC but not same from one implementation to another. + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion on next alignment call that takes place 13th April 2023. diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4639992f7412b80dbb4481c6e0866f1977c2e961 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week20_syncCalls.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4bc16d0e1e7c45a108ac368ad066ec354b9d5266 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week22_syncCalls.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..781b58c433f89b8f85172128ff1fe8160a66058f --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week24_syncCalls.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..29f94863f6102e0436cc97e3758804e9de8c7bc5 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week26_syncCalls.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..1d84b85d7c194a18be538340bb13b029b3cb57b5 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week28_syncCalls.md @@ -0,0 +1,47 @@ +Hmmm# Week 28 meeting + +## Participants + +13th July 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue [#33](https://github.com/camaraproject/NumberVerification/issues/33) - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..bfcff40a9b4d184e1e31063cec0dd15c5625b4fe --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week2_syncCalls.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delivered + +### NumberVerify + +- CAMARA & MC APIs yaml files delivered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..dbaf949d9342dc586b323020dd24d58af93a054c --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week32_syncCalls.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71e4117b347508f92e11b975698fad270626d34e --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week36_syncCalls.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ef5342ee522e0fba8d0eb487ef07eabb7eeb0dec --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week38_syncCalls.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ae2c49ba5cbbca3cfc4c0e9c8f2843d0f117ef11 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week40_syncCalls.md @@ -0,0 +1,65 @@ +# Week 38 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71b83502cdd314d2723ed46f852e4e1e6cad899b --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2023_Week42_syncCalls.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..2e87b4b18e751b1dfca19d0ccbff58516a21703b --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week10_syncCalls.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4d21478b982bd60ae559d9aa4e6398cf0949b7ff --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week12_syncCalls.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..0d3113d9a121a5cfefa735d20a647e062a863fc2 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week2_syncCalls.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..8231efe5770b6d7f1e29a80710342d8b0f24bf64 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week4_syncCalls.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..19743e011db7ad07aa92771cdc1e939d4a6ac552 --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week6_syncCalls.md @@ -0,0 +1,40 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB +* discussion about MWC 2024 +* add commits to sub-projects for next release +## APs diff --git a/original/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls.md b/original/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..04cbf65fda5ec2212f67cc70bf17681e3866c51a --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/2024_Week8_syncCalls.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/original/OTPValidation/documentation/MeetingMinutes/README.MD b/original/OTPValidation/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..10f865e83defa03b5e249d234ce3ff1e1604ffac --- /dev/null +++ b/original/OTPValidation/documentation/MeetingMinutes/README.MD @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [OTP Validation Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/OTP+Validation) \ No newline at end of file diff --git a/original/OTPValidation/documentation/SupportingDocuments/README.MD b/original/OTPValidation/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..38efecab2903648866bb8d5f867fab0e77ea71c6 --- /dev/null +++ b/original/OTPValidation/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +Here you can add your supporting documents and delete this README.MD file diff --git a/original/OptimalEdgeDiscovery/README.md b/original/OptimalEdgeDiscovery/README.md new file mode 100644 index 0000000000000000000000000000000000000000..211b9d402a22f1306b7991d1921bd8aa72549adb --- /dev/null +++ b/original/OptimalEdgeDiscovery/README.md @@ -0,0 +1,53 @@ +
                                                              + + + + + + + + +# OptimalEdgeDiscovery + +Sandbox API Repository to describe, develop, document, and test the OptimalEdgeDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AYAtC) + +## Scope + +* Service API(s) “OptimalEdgeDiscovery” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Discover the optimal regions and zones for their edge cloud application +* Describe, develop, document, and test the API(s) +* Started: July 2022 (in [EdgeCloud](https://github.com/camaraproject/EdgeCloud) repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/OptimalEdgeDiscovery/releases/tag/r1.2) (Fall25), with the following API versions: + * **optimal-edge-discovery v0.1.0** + [[YAML]](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/r1.2/code/API_definitions/optimal-edge-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/OptimalEdgeDiscovery/r1.2/code/API_definitions/optimal-edge-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/OptimalEdgeDiscovery/r1.2/code/API_definitions/optimal-edge-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/OptimalEdgeDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/OptimalEdgeDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/OptimalEdgeDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Bi-weekly on Tuesdays 14:00 - 15:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91868502920?password=a9ec9dff-ea92-4216-b0a1-ce152f49170f) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/OptimalEdgeDiscovery/code/API_definitions/README.MD b/original/OptimalEdgeDiscovery/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/OptimalEdgeDiscovery/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery.yaml b/original/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery.yaml new file mode 100644 index 0000000000000000000000000000000000000000..4228ca851749a5032434352c188dab6a12bc47d8 --- /dev/null +++ b/original/OptimalEdgeDiscovery/code/API_definitions/optimal-edge-discovery.yaml @@ -0,0 +1,840 @@ +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Optimal Edge Discovery + version: wip + x-camara-commonalities: 0.6 + description: | + # Introduction + --- + The Optimal Edge Discovery API is designed to help users discover the + optimal edge cloud zones for their applications. This API allows users to + find the optimal regions and zones to deploy their edge cloud applications + based on the device's location, network characteristics and the application + profile. + + ## Features + - Discover regions and zones to deploy edge cloud applications. + + ## Usage + Users can utilize this API to enhance the performance and connectivity of + their applications by selecting the most suitable edge cloud zones and + application endpoints. + + These APIs may be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet) or by the application + server for following scenarios: + + - **Edge Cloud Region Discovery**: To discover the regions where edge + cloud zones are available. Developers can use this information to + understand the geographical coverage of edge cloud services before + deciding where to deploy their applications or before using the more + specific optimal edge discovery functionality. + This can be achieved using the `/regions` API. + + - **Edge Cloud Zone Discovery**: To find the optimal edge cloud + zones to deploy application to minimize latency for users in a specific + region. This can be achieved using the + `/retrieve-optimal-edge-cloud-zones` API. + + To call these endpoints, the API consumer must first obtain a valid OAuth2 token + from the token endpoint, and pass it as an `Authorization` header in the API + request. + + # Identifying the device + + The API returns the closest Edge Cloud Zone to a given device, so that + device needs to be identifiable by the network. This can be achieved either + by passing one or more device identifiers in the request, or, from the + three-legged access token where implemented by the operator. + + ## Passing device identifier(s) in the request + At least one of the following device identifiers must be provided, unless + using a 3-legged access toekn (see next section): + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + + NOTE1: the network operator might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the + same device. + + NOTE2: for this Commonalities release, we are enforcing that the + `networkAccessIdentifier` is only part of the schema for future-proofing, and + CAMARA does not currently allow its use. After the CAMARA meta-release work + is concluded and the relevant issues are resolved, its use will need to be + explicitly documented in the guidelines. + + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will be + identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier + MUST NOT be provided, as the subject will be uniquely identified from the access + token. + + This approach simplifies API usage for API consumers using a three-legged access + token to invoke the API by relying on the information that is associated with the + access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` + object is not included in the request, then the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` + object is also included in the request, then the server will return an error with the + `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device + is identified by these two methods, as the server is unable to make this comparison. + + # Responses + + ## Success + + A JSON object is returned containing an array with a single member object. + This contains identifiers for the closest Edge Cloud Zone. The HTTP status + code will be`200 OK`. An example response: + + ``` + { + "edgeCloudZones": [ + { + "edgeCloudZoneId": "7ab123-9087-6543-ef12-3dc45f67gh89", + "edgeCloudZoneName": "Example Zone Name", + "edgeCloudProvider": "Example Zone Provider", + "edgeCloudRegion": "us-west-1", + "edgeCloudZoneStatus": "active" + } + ], + "applicationProfileId": "2fa85f64-5717-4562-b3fc-2c963f66afa0", + "device": { + "phoneNumber": "+123456789" + } + } + ``` + * `edgeCloudZoneId` is a UUID for the Edge Cloud Zone. + * `edgeCloudZoneName` is the common name of the closest Edge Cloud Zone to + the user device. + * `edgeCloudProvider` is the name of the operator or cloud provider of + the Edge Cloud Zone. + * `edgeCloudRegion` is the region of the closest Edge Cloud Zone to + the user device. + * `edgeCloudZoneStatus` is the status of the Edge Cloud Zone (default is 'unknown'). + * `edgeCloudZones` is an array of Edge Cloud Zones that match the query + parameters. The array will contain at least one Edge Cloud Zone, and + may contain multiple Edge Cloud Zones if there are multiple zones that + match the query parameters. + * `applicationProfileId` is the reference ID associated with the + application profile. This is a UUID that identifies the application + profile for which the Edge Cloud Zones are being discovered. + * `device` is an object containing the device identifier used to + determine the user's location. This object will contain one of the + following identifiers: + - `phoneNumber`: The phone number of the device in E.164 format. + - `networkAccessIdentifier`: The network access identifier assigned by + the mobile network operator for the device. + - `ipv4Address`: The public IPv4 address and port of the device. + - `ipv6Address`: The public IPv6 address of the device. + The response will contain only one of these identifiers, depending on + which identifier was used to identify the device in the request. + If the device was identified from the access token, the `device` object + will not be present in the response, and the `applicationProfileId` will + be the only field returned. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the `API + Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Notes for Optimal Edge Discovery API publishers + + Should your implementation require the `Port` value to be passed in addition + to the `IP-Address`, please make that explicit in the documentation, and + utilise the `GENERIC_400_MISSING_PORT` error if the `Port` header is + omitted. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to + Identity and Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the + API provider, taking into account the declared purpose for accessing the + API, whilst also being subject to the prevailing legal framework dictated + by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + --- + + license: + name: Apache 2.0 + url: "https://www.apache.org/licenses/LICENSE-2.0.html" +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/OptimalEdgeDiscovery + +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/optimal-edge-discovery/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` +############################################################################ +# Tags # +############################################################################ +tags: + - name: Regions + description: | + Get all Region IDs and Names for edge cloud zones + - name: Discovery + description: | + Discover the regions and zones in the edge cloud + application, find optimal edge cloud zones for + your deployed applications, and optimal + Application Endpoints for your clients to connect to. +############################################################################ +# Paths # +############################################################################ +paths: + /regions: + get: + summary: Fetch all Regions + operationId: getRegions + security: + - openId: + - "optimal-edge-discovery:regions:read" + parameters: + - $ref: "#/components/parameters/x-correlator" + responses: + '200': + description: Returns Edge Cloud Regions + content: + application/json: + schema: + title: GetEdgeCloudRegionsResponse + type: array + items: + $ref: "#/components/schemas/EdgeCloudRegion" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Regions + description: | + This is a helper API to get all the regions. The response identifies the + regions where edge cloud zones are available. + /retrieve-optimal-edge-cloud-zones: + post: + operationId: discoverOptimalEdge + security: + - openId: + - "optimal-edge-discovery:edge-zones:read" + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: false + content: + application/json: + schema: + $ref: "#/components/schemas/OptimalEdgeDiscoveryInfo" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + description: returns optimal edge cloud zone matching query + parameters + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/EdgeDiscoveryResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + tags: + - Discovery + summary: Discover optimal edge cloud zones for deployed applications + description: Returns a list of optimal edge cloud zones where you can + register your deployed application. You can choose to search without + passing any of the inputs parameters or a combination of Application + Profile and device information. + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + EdgeDiscoveryResponse: + type: object + description: | + Response for the optimal edge discovery API. It contains a list of + edge cloud zones that match the query parameters. + properties: + edgeCloudZones: + type: array + items: + $ref: "#/components/schemas/EdgeCloudZone" + minItems: 1 + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/DeviceResponse" + + EdgeCloudZone: + type: object + description: Edge cloud zone information for the + given application profile and device information + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudZoneStatus: + $ref: "#/components/schemas/EdgeCloudZoneStatus" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + + ApplicationProfileId: + type: string + format: uuid + description: reference id associated to application profile + + EdgeCloudZoneId: + description: | + Operator-issued UUID for the Edge Cloud Zone. + type: string + format: uuid + additionalProperties: false + + EdgeCloudZoneName: + description: | + The name of the operator or cloud provider of the Edge Cloud Zone. + type: string + additionalProperties: false + + EdgeCloudProvider: + description: | + The company name of the Edge Cloud Zone provider. + type: string + + EdgeCloudRegion: + description: | + The common name of the closest Edge Cloud Zone to the user device. + type: string + example: "us-west-1" + + EdgeCloudZoneStatus: + description: Status of the Edge Cloud Zone (default is 'unknown') + type: string + enum: + - active + - inactive + - unknown + default: unknown + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + OptimalEdgeDiscoveryInfo: + description: | + Resource to obtain the optimal edge cloud zone for a given application + profile and device information. The API returns the closest Edge Cloud + Zone to a given device, so the device needs to be identifiable by the + network. This can be achieved either by passing a device identifier in + the request header, or, from the 3-legged access token where implemented + by the operator. + type: object + properties: + device: + $ref: "#/components/schemas/Device" + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + edgeCloudRegion: + $ref: "#/components/schemas/EdgeCloudRegion" + required: + - applicationProfileId + + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their + request, the API provider must return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do not + match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers + with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. + Examples of devices include smartphones or IoT sensors/actuators.The + developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the network operator might support only a subset of these options + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for future-proofing, + and CAMARA does not currently allow its use. After the CAMARA + meta-release work is concluded and the relevant issues are resolved, + its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: A public identifier addressing a telephone subscription. + In mobile networks it corresponds to the MSISDN + (Mobile Station International Subscriber Directory Number). In order to + be globally unique it has to be formatted in international format, + according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a + mobile network. In 3GPP terminology, it corresponds to the GPSI + formatted with the External Identifier + ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, + the network access identifier is not subjected to portability ruling in + force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) + IP address and port as seen by the application server, or the + private (local) and any public (observed) IP addresses in use by the + device (this information can be obtained by various means, for example + from some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. If NAT64 is in use, the device should + be identified by its publicAddress and publicPort, or separately by its + allocated IPv6 address (field ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ###################################################### + # RESPONSES + ####################################################### + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, + request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has a pre-defined range or a invalid filter criteria + combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new + authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or + expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to + perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in + some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the + device or phone number identification cannot be derived from the + 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is + supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or + phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a + business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due + to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + applicationProfileId: "2fa85f64-5717-4562-b3fc-2c963f66afa0" + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" diff --git a/original/OptimalEdgeDiscovery/documentation/API_documentation/README.MD b/original/OptimalEdgeDiscovery/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/OptimalEdgeDiscovery/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist.md b/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..86d6c06ca38291e9105f9f5f61b0dcde15997f73 --- /dev/null +++ b/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# Optimal Edge Discovery API Readiness minimum criteria checklist + +Checklist for Optimal-Edge-Discovery v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                              public | stable
                                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/optimal-edge-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/optimal-edge-discovery-User-Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/optimal-edge-discovery.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/N4AtC) | diff --git a/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story.md b/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story.md new file mode 100644 index 0000000000000000000000000000000000000000..db50fd4d0b475663f786170902f0142e65c53689 --- /dev/null +++ b/original/OptimalEdgeDiscovery/documentation/API_documentation/optimal-edge-discovery-User-Story.md @@ -0,0 +1,10 @@ +# Optimal Edge Discovery API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer, I need to discover the optimal Edge Cloud Zones for deploying my application instances, ensuring my users get the best performance by connecting to edge resources with minimal latency. The Optimal Edge Discovery API allows me to find the Edge Cloud Zones that are closest to a specific device, providing information about their locations, capabilities, and network characteristics. This helps me make informed decisions about where to deploy my application instances to ensure optimal performance for users across different geographical areas. | +| ***Roles, Actors and Scope*** | **Roles:** API Consumer:Developer
                                                              **Actors:** Application service providers, hyperscalers, application developers. Currently the API does not explicitly handle consent management (expects that the API consumer either owns the device subscriptions or has agreed to manage consent as a part of general Terms and Conditions) and hence end users are not included as Actors. As this changes, the actor list will be extended with end users.
                                                              **Scope:**
                                                              • Discover optimal Edge Cloud Zones for specific devices
                                                              • Retrieve information about available Edge Cloud Zones and their capabilities
                                                              • Make informed decisions about application deployment locations
                                                              | +| ***Pre-conditions*** |The preconditions are listed below:
                                                              1. The API Consumer:BusinessManager and API Consumer:Administrator have been onboarded to the API Exposure Platform.
                                                              2. The API Consumer:BusinessManager has successfully subscribed to the Optimal Edge Discovery product from the product catalog.
                                                              3. The API Consumer:Administrator has onboarded the developer:User to the platform.
                                                              4. The API Consumer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                                                              5. The means to get the access token are known to the API Consumer:User to ensure secure access of the API.
                                                              | +| ***Activities/Steps*** | **Starts when:**
                                                              1. The API consumer application makes a request to discover the optimal Edge Cloud Zones for a specific device, optionally providing filter parameters to narrow down the results.

                                                              **Ends when:**
                                                              1. The API endpoint returns information about available Edge Cloud Zones ordered by their proximity to the device. | +| ***Post-conditions*** | 1. The API consumer has information about optimal Edge Cloud Zones for deploying their application instances.
                                                              2. The API consumer can use this information to make decisions about application deployment or to register application endpoints in these zones. | +| ***Exceptions*** | Several exceptions might occur
                                                              - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                              - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                                                              - Invalid filter: The filter parameters provided are not valid or cannot be applied.
                                                              - Not Found: No Edge Cloud Zones are available that match the specified criteria.
                                                              - Identifier Not Found: The device identified in the request cannot be found in the network. diff --git a/original/OptimalEdgeDiscovery/documentation/SupportingDocuments/README.MD b/original/OptimalEdgeDiscovery/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/OptimalEdgeDiscovery/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/PopulationDensityData/README.md b/original/PopulationDensityData/README.md new file mode 100644 index 0000000000000000000000000000000000000000..f19be359747b4b6029dfec0273218a2de9b1a78a --- /dev/null +++ b/original/PopulationDensityData/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# PopulationDensityData + +Incubating API Repository to evolve and maintain the definitions and documentation of PopulationDensityData Service API(s) within the Sub Project [Population Density Data](https://lf-camaraproject.atlassian.net/wiki/x/LwAwC) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/3DXe) + +## Scope +* Service APIs for “Population Density Data” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * The service enables developers with the capability to get dynamic population density data in a specific area for a specified date&time, considering anonymized information of the network connected devices in the requested area at the flight time. + * Use Case (1): Providing BVLOS flight the data to meet SORA 2.5 requirements in terms of intrinsic Ground Risk Class (iGRC). + * Use Case (2): Providing data to identify if the ground risk class for a given drone flight is acceptable for the time of the flight, or an alternative time should be considered to lower the risk. + * Service Inputs: Area of the interest. Date & time range. + * Service Outputs: maximum, average and minimum population density value for the given area, and interval corresponding to the valid range of that value. (space and time maps). + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Incubating stage since: June 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/PopulationDensityData/releases/tag/r3.2) (Fall25), with the following API versions: + * **population-density-data v0.3.0** + [[YAML]](https://github.com/camaraproject/PopulationDensityData/blob/r3.2/code/API_definitions/population-density-data.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/PopulationDensityData/r3.2/code/API_definitions/population-density-data.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/PopulationDensityData/r3.2/code/API_definitions/population-density-data.yaml) +* The latest public release is always available here: https://github.com/camaraproject/PopulationDensityData/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/PopulationDensityData/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/PopulationDensityData/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Wednesday, 14:00 Europe/Amsterdam (CET) (13:00 UTC, 12:00 UTC during European DST). + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95956472717?password=e4e7e889-ffb8-4fac-9e9d-d9adcaf2e711) + * For date/time of next meeting see previous [ meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/HwPe) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/PopulationDensityData/code/API_definitions/population-density-data.yaml b/original/PopulationDensityData/code/API_definitions/population-density-data.yaml new file mode 100644 index 0000000000000000000000000000000000000000..8966b519a368f76bb6ba7d2528096154619666c1 --- /dev/null +++ b/original/PopulationDensityData/code/API_definitions/population-density-data.yaml @@ -0,0 +1,1132 @@ +openapi: 3.0.3 +info: + title: Population Density Data + description: >- + The Population Density Data API exposes population density estimations + for a specified area for a specified time interval. + + # Introduction + + With the Population Density Data API the customer can retrieve population density estimations + for a specific area at the current or a specified period of time. The estimation considers historical + anonymized information of the network connected devices in the requested + area. * Note that the data provided are estimations of population, based on past or future predicted data, for both past or future time ranges. + + + This functionality can be used for multiple use + cases, some of the possible use cases for this API are: + + + - Supporting BVLOS (Beyond Visual Line of Sight) flights with the + information needed to meet SORA 2.5 (Specific Operation Risk Assessment) + requirements in terms of intrinsic Ground Risk Class (iGRC). + More information in [Specific Operations Risk Assessment](https://www.easa.europa.eu/en/domains/civil-drones-rpas/specific-category-civil-drones/specific-operations-risk-assessment-sora) + + - Providing information to identify if the ground risk class for + a given drone flight path is acceptable for the time of the flight, or an + alternative time should be considered to lower the risk. + + - Sustainable Urban Planning. + + - Environmental monitoring at mass events, such as concerts or festivals. + + + The list above is just a few examples, the API can be used for other use cases as well. + + + # Relevant terms and definitions + + * **Population Density**: refers to the number of people in a given area divided by the total size of the area. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. + This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + When an asynchronous response is requested, the 202 response of the API will include an `operationId` property. This `operationId` property will + also be sent in the callback notification. The purpose of the `operationId` is to correlate an asynchronous response with its corresponding request. + + # API Functionality + + Once a developer specifies (1) the area as a polygon shape, (2) a precision level and (3) time interval + in which they want to obtain the population density, the API returns a data + set consisting of a sequence of time ranges, with each time range containing the + input polygon subdivided into equal-sized grid cells. + + + For each of the equal-sized cells of the grid, an estimated population density is + reported for each time slot within the range, this includes: estimated population density people/km2, and a range for this estimation - [minimum, maximum] + (exact definitions of minimum and maximum are estimation algorithm specific). + + + These values are calculated based on historical data, prediction models, and population estimation models. The requested interval must either be completely in the future or in the past. + + The API has the following time constraints for requests: the minimum startTime must cover at least 3 months before the request time, + and the maximum endTime allowed is 3 months from the time of the request. + + The polygon specifying an area of interest must comply with certain restrictions, + which must be previously validated by the developer: + + - The polygon may not exceed a certain area. + + - The polygon may not contain more than 15 vertexes. + + - The polygon must be associated with a location where the MNO provides + mobile connectivity services. If a polygon is located entirely outside the + supported area, an empty array is returned. + + + The standard behaviour of the API is synchronous, although for large + area requests the API may behave asynchronously. An API invoker can enforce + asynchronous behaviour by providing a callback URL (`sink`) + is in the request, in this case the API sends a callback + to the callback URL provided with the result of the request. If `sink` is + included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` + MUST be set to `ACCESSTOKEN` if provided. + + + For requests with a combination of `area`, `precision`, `startTime` and `endTime` + properties involving an amount of processing that cannot be processed synchronously, + the API returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE`. + + + For requests with a combination of `area`, `precision`, `startTime` and `endTime` + properties too big for both synchronous and asynchronous processing, the API + returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST`. + + If an error happens during the asynchronous processing of the request. The API callback + will have property `status` with value `OPERATION_NOT_COMPLETED` as an error cannot be returned in the callback. + The callback will also include the `statusInfo` property to add extra information about the error. + + **NOTE**: In order to ensure anonymized information, if the data relating to + a grid cell in the required time interval is not sufficient to be exposed due + to [k-anonymity](https://en.wikipedia.org/wiki/K-anonymity), no such data is + returned by the API and the value of the dataType property is `LOW_DENSITY`. + + # Resources and Operations overview + + The API provides one endpoint that accepts POST requests for retrieving population + density information in the specified area. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Population Density Data API ensures the usage of anonymized information and do not treat personal data neither as input nor output. + Therefore, the access to Population Density Data API is defined as Client Credentials - 2-legged. Please refer to Identify and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/PopulationDensityData + +servers: + - url: '{apiRoot}/population-density-data/vwip' + + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Population Density Data + description: Operations to retrieve population density information. +paths: + /retrieve: + post: + tags: + - Population Density Data + summary: Retrieves population density information in a specified area + description: >- + Retrieves population density estimation together with the estimation range related + for a time slot for a given area (described as a polygon) as a data set + consisting of a sequence of equally-sized objects covering the input + polygon area. + operationId: retrievePopulationDensity + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityRequest' + example: + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.75249 + longitude: 4.861876 + - latitude: 45.751224 + longitude: 4.861125 + - latitude: 45.751442 + longitude: 4.859827 + startTime: '2024-04-23T14:44:18.165Z' + endTime: '2024-04-23T14:44:18.165Z' + precision: 7 + required: true + callbacks: + populationDensityDataCallback: + '{$request.body#/sink}': + post: + tags: + - Population Density Data + summary: 'Population Density Data callback' + description: | + Important: this endpoint is to be implemented by the API consumer. + The Population Density Data server will call this endpoint when the request result is ready. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Population density data result. + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityAsyncResponse' + examples: + PopulationDensitySupportedAreaAsyncResponseExample: + $ref: '#/components/examples/PopulationDensitySupportedAreaAsyncResponseExample' + PopulationDensityAreaNotSupportedAsyncResponseExample: + $ref: '#/components/examples/PopulationDensityAreaNotSupportedAsyncResponseExample' + PopulationDensityPartOfAreaNotSupportedAsyncResponseExample: + $ref: '#/components/examples/PopulationDensityPartOfAreaNotSupportedAsyncResponseExample' + PopulationDensityOperationNotCompletedExample: + $ref: '#/components/examples/PopulationDensityOperationNotCompletedExample' + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + '429': + $ref: '#/components/responses/Generic429' + security: + - {} + - notificationsBearerAuth: [] + responses: + '200': + description: Population density data result. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/PopulationDensityResponse' + examples: + PopulationDensitySupportedAreaResponseExample: + $ref: '#/components/examples/PopulationDensitySupportedAreaResponseExample' + PopulationDensityAreaNotSupportedResponseExample: + $ref: '#/components/examples/PopulationDensityAreaNotSupportedResponseExample' + PopulationDensityPartOfAreaNotSupportedResponseExample: + $ref: '#/components/examples/PopulationDensityPartOfAreaNotSupportedResponseExample' + + '202': + description: Population density data requested. This response is returned when the behaviour of the API is asynchronous. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AcceptedAsyncResponse' + '400': + $ref: '#/components/responses/RetrieveLocationBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/RetrieveLocationUnprocessableContent422' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - population-density-data:read +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: '{$request.body#sinkCredential.credentialType}' + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PopulationDensityRequest: + type: object + description: >- + Request object for retrieving population density data in a + specified area. + **NOTE**: The difference between `startTime` and `endTime` cannot be greater than 7 days. + properties: + area: + $ref: '#/components/schemas/Area' + startTime: + type: string + format: date-time + description: >- + Start date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + example: "2023-07-03T12:27:08.312Z" + endTime: + type: string + format: date-time + description: >- + End date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + The maximum endTime allowed is 3 months from the time of the request. + example: "2023-07-03T12:27:08.312Z" + precision: + type: integer + description: >- + Precision required of response cells. Precision defines a geohash level and corresponds to the length of the geohash for each cell. More information at [Geohash system](https://en.wikipedia.org/wiki/Geohash)" + If not included the default precision level 7 is used by default. In case of using a not supported level by the MNO, the API returns the error response `POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION`. + minimum: 1 + maximum: 12 + default: 7 + sink: + type: string + format: uri + description: The address where the API response will be asynchronously delivered, using the HTTP protocol. + pattern: ^https:\/\/.+$ + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + required: + - area + - startTime + - endTime + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + POLYGON - The area is defined as a polygon. + enum: + - POLYGON + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + PopulationDensityResponse: + type: object + description: >- + Population density values is represented in time intervals for different + cells of the requested area. Each element in `timedPopulationDensityData` array corresponds + to a time interval, containing population density data for the grid cells. The intervals are 1 hour long. + properties: + timedPopulationDensityData: + type: array + description: >- + Time ranges along with the population density data for the cells within it. + The request startTime or the request endTime have to be fully covered by the intervals. + For example, if the intervals are 1-hour long and the input date range were [2024-01-03T11:25:00Z + to 2024-01-03T12:45:00Z] it would contain 2 intervals (Interval from 2024-01-03T11:00:00Z + to 2024-01-03T12:00:00Z and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + items: + $ref: '#/components/schemas/TimedPopulationDensityData' + status: + $ref: '#/components/schemas/ResponseStatus' + statusInfo: + type: string + description: Information about the status, mandatory when property `status` is `OPERATION_NOT_COMPLETED` for adding extra information about the error. + example: Some error happened during the processing of the request + required: + - timedPopulationDensityData + - status + AcceptedAsyncResponse: + type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + PopulationDensityAsyncResponse: + allOf: + - $ref: '#/components/schemas/PopulationDensityResponse' + - type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + OperationId: + type: string + description: The unique identifier of the asynchronous operation that is returned when the operation is initiated. + ResponseStatus: + type: string + description: >- + Represents the state of the response for the input polygon defined in the request, the possible values are: + - `SUPPORTED_AREA`: The whole request area is supported. Population density data for the entire requested area is returned. + - `PART_OF_AREA_NOT_SUPPORTED`: Part of the requested area is outside the MNOs coverage area, the cells outside the coverage + area will have property `dataType` with value `NO_DATA`. + - `AREA_NOT_SUPPORTED`: The whole requested area is outside the MNOs coverage area. No data will be returned. + - `OPERATION_NOT_COMPLETED`: An error happened during asynchronous processing of the request. This status will only be returned + in case the asynchronous API behaviour is used. + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - OPERATION_NOT_COMPLETED + TimedPopulationDensityData: + type: object + properties: + startTime: + type: string + format: date-time + description: >- + Interval start time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T10:00:00Z" + endTime: + type: string + format: date-time + description: >- + Interval end time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ + (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T11:00:00Z" + cellPopulationDensityData: + $ref: '#/components/schemas/CellPopulationDensityDataArray' + required: + - startTime + - endTime + - cellPopulationDensityData + CellPopulationDensityDataArray: + type: array + description: >- + Population density data for the different cells in a concrete time range. + items: + $ref: '#/components/schemas/CellPopulationDensityData' + minItems: 1 + CellPopulationDensityData: + type: object + description: >- + Population density data of a cell in a concrete time range. In case of + insufficient data, to guarantee an anonymized prediction due to the + k-anonymity within a specific cell and time range, no population density + data is returned and the property `dataType` value is "LOW_DENSITY". In + case of a cell not supported `dataType` value is "NO_DATA" + properties: + geohash: + type: string + description: >- + Coordinates of the cell represented as a string using the [Geohash system](https://en.wikipedia.org/wiki/Geohash). + Encoding a geographic location into a short string. The value length, + and thus, the cell granularity, is determined by the request body property `precision`. + example: ezdmemd + dataType: + type: string + enum: + - NO_DATA + - LOW_DENSITY + - DENSITY_ESTIMATION + required: + - geohash + - dataType + discriminator: + propertyName: dataType + mapping: + NO_DATA: '#/components/schemas/NoData' + LOW_DENSITY: '#/components/schemas/LowDensity' + DENSITY_ESTIMATION: '#/components/schemas/DensityEstimation' + NoData: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + LowDensity: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + DensityEstimation: + allOf: + - $ref: '#/components/schemas/CellPopulationDensityData' + - type: object + properties: + maxPplDensity: + type: integer + description: Maximum people/km2 estimated for the defined area. + minPplDensity: + type: integer + description: Minimum people/km2 estimated for the defined area. + pplDensity: + type: integer + description: people/km2 estimation for the defined area. + required: + - maxPplDensity + - minPplDensity + - pplDensity + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + RetrieveLocationBadRequest400: + description: >- + Problem with the client request. In addition to generic scenarios of + `INVALID_ARGUMENT`, `INVALID_CREDENTIAL`, `INVALID_TOKEN`, another scenarios may exist: + - The area is not a polygon shape or exceeds supported complexity ("code": "POPULATION_DENSITY_DATA.INVALID_AREA", "message": "The area is not a polygon shape or exceeds supported complexity") + - Indicated `startTime` is greater than the maximum allowed ("code": "POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED", "message": "Indicated startTime is greater than the maximum allowed") + - Indicated `startTime` is earlier than the minimum allowed ("code": "POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED", "message": "Indicated startTime is earlier than the minimum allowed") + - Indicated `endTime` is earlier than the `startTime` ("code": "POPULATION_DENSITY_DATA.INVALID_END_TIME", "message": "Indicated endTime is earlier than the startTime") + - Indicated time period is partially in the past and partially in the future ("code": "POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD", "message": "time period is partially in the past and partially in the future") + - Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime) ("code": "POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED", "message": "Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime)") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + - POPULATION_DENSITY_DATA.INVALID_AREA + - POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED + - POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED + - POPULATION_DENSITY_DATA.INVALID_END_TIME + - POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED + - POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Invalid input + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + POPULATION_DENSITY_DATA_400_INVALID_AREA: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_AREA + message: The area is not a polygon shape or has an arbitrary complexity + POPULATION_DENSITY_DATA_400_MAX_STARTTIME_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MAX_STARTTIME_EXCEEDED + message: >- + Indicated startTime is greater than the maximum allowed + POPULATION_DENSITY_DATA_400_MIN_STARTTIME_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MIN_STARTTIME_EXCEEDED + message: >- + Indicated startTime is earlier than the minimum allowed + POPULATION_DENSITY_DATA_400_INVALID_END_TIME: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_END_TIME + message: Indicated endDate is earlier than the startTime + POPULATION_DENSITY_DATA_400_MAX_TIME_PERIOD_EXCEEDED: + value: + status: 400 + code: POPULATION_DENSITY_DATA.MAX_TIME_PERIOD_EXCEEDED + message: >- + Indicated time period is greater than the maximum allowed + (More than maximum hours between startTime and endTime) + POPULATION_DENSITY_DATA_400_INVALID_TIME_PERIOD: + value: + status: 400 + code: POPULATION_DENSITY_DATA.INVALID_TIME_PERIOD + message: >- + Indicated time period is partially in the past and partially in the future + + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + RetrieveLocationUnprocessableContent422: + description: >- + Problem with the client request. The following scenarios may exist: + - Indicated combination of area, time interval and precision is too big ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST", "message": "Indicated combination of area, time interval and precision is too big") + - Indicated cell precision (Geohash level) is not supported ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION", "message": "Indicated cell precision (Geohash level) is not supported") + - Indicated combination of area, time interval and precision is too big for a sync response ("code": "POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE", "message": "Indicated combination of area, time interval and precision is too big for a sync response") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST + - POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION + - POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE + examples: + POPULATION_DENSITY_DATA_422_UNSUPPORTED_REQUEST: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_REQUEST + message: Indicated combination of area, time interval and precision is too big for both synchronous and asynchronous processing + POPULATION_DENSITY_DATA_422_UNSUPPORTED_PRECISION: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_PRECISION + message: >- + Indicated cell precision (Geohash length) is not supported + POPULATION_DENSITY_DATA_422_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 422 + code: POPULATION_DENSITY_DATA.UNSUPPORTED_SYNC_RESPONSE + message: >- + Indicated combination of area, time interval and precision is too big for synchronous processing + and asynchronous processing is not enabled + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + PopulationDensitySupportedAreaResponseExample: + value: + status: SUPPORTED_AREA + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: LOW_DENSITY + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + PopulationDensityPartOfAreaNotSupportedResponseExample: + value: + status: PART_OF_AREA_NOT_SUPPORTED + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: NO_DATA + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: NO_DATA + PopulationDensityAreaNotSupportedResponseExample: + value: + status: AREA_NOT_SUPPORTED + timedPopulationDensityData: [] + PopulationDensitySupportedAreaAsyncResponseExample: + value: + status: SUPPORTED_AREA + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: LOW_DENSITY + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityPartOfAreaNotSupportedAsyncResponseExample: + value: + status: PART_OF_AREA_NOT_SUPPORTED + timedPopulationDensityData: + - startTime: '2024-01-03T10:00:00Z' + endTime: '2024-01-03T11:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 150 + minPplDensity: 30 + pplDensity: 60 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 40 + pplDensity: 90 + - geohash: ezdqemu + dataType: NO_DATA + - startTime: '2024-01-03T11:00:00Z' + endTime: '2024-01-03T12:00:00Z' + cellPopulationDensityData: + - geohash: ezdqemf + dataType: DENSITY_ESTIMATION + maxPplDensity: 100 + minPplDensity: 30 + pplDensity: 70 + - geohash: ezdqemg + dataType: DENSITY_ESTIMATION + maxPplDensity: 200 + minPplDensity: 40 + pplDensity: 100 + - geohash: ezdqemu + dataType: NO_DATA + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityAreaNotSupportedAsyncResponseExample: + value: + status: AREA_NOT_SUPPORTED + timedPopulationDensityData: [] + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + PopulationDensityOperationNotCompletedExample: + value: + status: OPERATION_NOT_COMPLETED + timedPopulationDensityData: [] + statusInfo: Some error happened during the processing of the request + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 diff --git a/original/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist.md b/original/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ed960f877555f62757a0ef31d06042a277ada154 --- /dev/null +++ b/original/PopulationDensityData/documentation/API_documentation/population-density-data-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for population-density-data 0.3.0 in release r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                              public | stable
                                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/population-density-data.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.2) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.2) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.3.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/population-density-data.yaml) | +| 6 | User stories | O | O | O | M | N | TBC | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/population-density-data.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/population-density-data.feature) | +| 9 | Test result statement | O | O | O | M | N | TBC | +| 10 | API release numbering convention applied | M | M | M | M | Y | r3.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | No | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/74448957/PopulationDensityData+API+description) | diff --git a/original/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02.md b/original/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02.md new file mode 100644 index 0000000000000000000000000000000000000000..0283f418f0eeba8d247c203481fcbffbe4cc3439 --- /dev/null +++ b/original/PopulationDensityData/documentation/MeetingMinutes/MeetingMinutes07-02.md @@ -0,0 +1,99 @@ +# CAMARA Population Density Data API - Follow-up meeting #1 - 2024-02-07 + +*February 07th, 2024* + +## Attendees + +|| +| --- | +|Sachin Kumar (Vodafone)| +|Thomas Neubauer (Dimetor)| +|Violeta Gonzalez Fernandez (Telefonica)| +|Jorge Garcia Hospital (Telefonica)| + + + +Population Density Data API minutes: [https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Approval of previous meeting minutes #1 and meeting agenda + * Confluence adoption +* Open issues and PRs + * Issues: #4 + * PRs: #3 #5 +* Timeline and next steps +* AoB + + +## Open Issues & PRs
                                                              + + +Item | Who | Description +---- | ---- | ---- +[PR#1](https://github.com/camaraproject/PopulationDensityData/pull/1) | Telefonica | Previous meeting material and minutes +[PR#2](https://github.com/camaraproject/PopulationDensityData/pull/2) | Telefonica | Readme update +[PR#3](https://github.com/camaraproject/PopulationDensityData/pull/3) | Verizon | Including new subgroup maintainer +[Issue#4](https://github.com/camaraproject/PopulationDensityData/issues/4) | Telefonica | Innitial scope agreement +[PR#5](https://github.com/camaraproject/PopulationDensityData/pull/5) | Telefonica | Innitial PopulationDensityData API spec proposal + +## Approval of previous meeting minutes & documentation (#1) + +[KO Meeting Minutes](https://github.com/camaraproject/PopulationDensityData/blob/main/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md) + +### Readme modifications (#2) + +Including the description of the group, link to minutes and schedule of the following meetings (also meeting link) + +### Confluence - to be agreed + +CAMARA is moving the documentation (meeting minutes mainly) to the [wiki.camaraproject.org](https://wiki.camaraproject.org/) Confluence webpage. Proposal to be agreed on moving meeting minutes for following meetings in that format from now on. + +Agreement: To be used from next meeting, minutes and agenda will be placed there. + +### New Maintainer (#3) + +Verizon proposed as new maintainer of the API subgroup. + +### API proposal review (#5) + +Different discussions raised during the API review: +* **Information in water zones**: Operators and therefore API can only provide data of those zones where it is operating. Water zones are not considered and current implementation will provive an error in case the requested zone includes a water zone. Dimetor proposes to only provide "nonData" or null response for those specific cells, but not a complete error, concious of the multiple cases where flights will indeed consider wateer zones due to the expected low population density. + +* Open discussion on **default and limit values** for the API characteristics: + * **Minimum and maximum date** minimum and maximum date allowed as requested time range. Currently, 15 minutes is set as the minimum (soonest time target the request can consider), and 1 year for maximum (longer date with information to extrapolate). TBD + + * **Time interval** in the request: Maximum (and minimum) lenght of the time range requested in the API. TBD + + * **Time granularity** in the response: Lenght of the information pieces in which the time interval is subdivided in the response. Default value is proposed in 1hour, so the response will include density information of each 1hour range that can be included in the requested interval. E.g. If request interval is 15minutes to 1 hour, 1 only result will be provided, if 3 hours and 45 minutes are requested, 4 results will be provided (from 0-1, 1-2, 2-3, 3-3:45). TBD + * **Cell size/granularity** in the response: Currently both cell definition systems allow to implement different size of cells. TBD + +* Cell's format in the response: Currently, API support two different formats of defining the cells in which the requested area is divided for providing the information in the response: + * **Boundary Cells**: The cell is defined by a polygon, composed by the internal area bounded by 4 geo positions. *Same solution as in Location Retrieval API + + * **Geohash Cells**: The Coordinates of the cell are representad as a string using the [Geohash system](https://en.wikipedia.org/wiki/Geohash). The value length, and thus the cell granularity, is determined by the implementation. + + Discussion on which mechanisms to restrict, or how to allow developers to select one of them if multiple are supported.\ + + *(Note that optionality in one side implies obligatory for the other, in this case forcing developers to support both options)* + +## Discussion + +Item | Discussion +---- | ---- +[PR#1](https://github.com/camaraproject/PopulationDensityData/pull/1) | Approval of previous meetinge minutes → Approved +[PR#2](https://github.com/camaraproject/PopulationDensityData/pull/2) | Confirmation of subgroup readme information → Noted +[PR#3](https://github.com/camaraproject/PopulationDensityData/pull/3) | Confirm Verizon as new maintainer → Noted +[Issue#4](https://github.com/camaraproject/PopulationDensityData/issues/4) | Close scope of the innitial API → Approved +[PR#5](https://github.com/camaraproject/PopulationDensityData/pull/5) | Review proposal of innitial API code → [Issue#6](https://github.com/camaraproject/PopulationDensityData/issues/6) [Issue#7](https://github.com/camaraproject/PopulationDensityData/issues/7) [Issue#8](https://github.com/camaraproject/PopulationDensityData/issues/8) Oppened for offline Oppened for offline discussion. +AoB | - + +## Next steps +1. Review and close open points PDD → Follow-up meeting #2 +2. Propose innitial draft of algorithm → Follow-up meeting #2 +3. Draft API spec agreement → Follow-up meeting #3 + + +- Next call will be **February 21th, 2024** + +

                                                              \ No newline at end of file diff --git a/original/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md b/original/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md new file mode 100644 index 0000000000000000000000000000000000000000..75cd69dd36be669e242ea36320f75fc18e55cfa0 --- /dev/null +++ b/original/PopulationDensityData/documentation/MeetingMinutes/PopulationDensityDataAPI-KOmeeting_2024-01-24.md @@ -0,0 +1,65 @@ +# CAMARA Population Density Data API - KO meeting - 2024-01-24 + +*January 24th, 2024* + +## Attendees + +|| +| --- | +|Sachin Kumar (Vodafone)| +|Thomas Wana (Dimetor)| +|Thomas Neubauer (Dimetor)| +|Violeta Gonzalez Fernandez (Telefonica)| +|Jorge Garcia Hospital (Telefonica)| + + + +Population Density Data API minutes: [https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Presentation of the working group + * Density Population Data reference use cases +* Schedule and bi-weekly planification +* Timeline and next steps +* AoB + + +## Open Issues & PRs
                                                              + + +Item | Who | Description +---- | ---- | ---- +N/A | N/A | N/A + +## Introduction to the working group + +Supporting material: [KO supporting material](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/SupportingDocuments/KO%20-%20Population%20Density%20Data%20Proposal%20for%20Camara%20Standarizationv3.pptx) + +### Scope + +**API definition:** The Population Density Data API enables developers with the capability to get population density estimations for a specific area at a future date and time, considering historical anonymized information of the network connected devices in the requested area. + +**API inputs (TBC):** Geographical area (2D map) and time range (future) + +**API outputs (TBC):** Max, min and average estimated statistics of population density for the required map, divided in uniform cells depending on the accuracy of the data. In a time series, to include information for the complete requested time range + + +### Density Population Data reference use cases + +For the reference use case, the API fills the need of assessing the ground risk to allow safe drone flights by providing estimations of the number of people under a drone flight path. This assessment will be needed every time a drone flight in the specific category need to conduct an operation and will help the operator to identify operational limitations, to develop the appropriate operational procedures and to identify mitigations and safety objectives. More information in [KO supporting material](https://github.com/camaraproject/PopulationDensityData/tree/main/documentation/SupportingDocuments/KO%20-%20Population%20Density%20Data%20Proposal%20for%20Camara%20Standarizationv3.pptx) + +## Discussion + +Item | Discussion +---- | ---- +Group Scope | Telefonica shares the proposal to include not only the specification of the API but also the agreement on the required algorithms of prediction and interpolation that are required in the API to provide a homogeneous response among operators. Aggrement reached. +Meeting Schedule | It's agreed to keep KO time schedule to be replicated in the following repetitions of the subgroup meetings.
                                                              Be-weekly meeting on Wednesday, 14:00 Europe/Amsterdam (CET) (13:00 UTC, 12:00 UTC during European DST), starting February, 7th. +Timeline and next steps | Schedule to close scope, prepare innitial yaml proposal and close RC version is proposed. +AoB | N/A + + + +- Next call will be **February 7th, 2024** + +

                                                              diff --git a/original/PopulationDensityData/documentation/MeetingMinutes/README.MD b/original/PopulationDensityData/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/PopulationDensityData/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal.md b/original/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal.md new file mode 100644 index 0000000000000000000000000000000000000000..e8d97f71a9a0311500545d806f877167ceae4238 --- /dev/null +++ b/original/PopulationDensityData/documentation/SupportingDocuments/Population_Density_API_-_Algorithm_Initial_Proposal.md @@ -0,0 +1,30 @@ +# Population Density Data API +## Algorithm initial proposal + +This document serves as a reference model for the population density calculation algorithm. It provides an illustrative high-level overview of the steps proposed to determine population density. Designed for developers, this guide is created to enhance understanding and implementation of the algorithm. While it aims to enhance understanding and implementation, it is the responsibility of the developer to create their own algorithm to calculate population density. + +### Inputs for the algorithm: +* Devices connection records data is received pseudonymized or hashed. +* Requested Space is received in the API customers’ request. +### Process is as follows: +

                                                                +
                                                              1. Cleanup: Considering one year of historical information, repeated records will be deleted and IOT (non-personal devices) lines records are filtered due to they do not contribute to the process of estimating future population density.
                                                                +Output 1 → Cleaned list of Devices connection records

                                                              2. +
                                                              3. Attribution: A cell is associated with each user in each time interval. +
                                                                1. For mobile lines with persistent records, the last cell in which each user has been connected in each interval (considering intervals of 15 minutes) will be associated.
                                                                2. +
                                                                3. It is common to have intervals for which a user does not show activity, for them it will be assumed that the user remains in the same cell in which he was last seen active.
                                                                +Output 2 → Valid Users per cell in each time interval

                                                              4. +
                                                              5. Counting and Aggregation: A count of users is performed per cell and interval. On this count, a statistical analysis is performed with the elimination of outliers. Records associated with cells with less than K users in each time interval (k – anonymity) per km2 are discarded (to be evaluated according to local regulations).
                                                                +Output 3 → Total number of Users connected per cell in each time interval, considering privacy.

                                                              6. +
                                                              7. Spatial indexing (no personal data is processed): the space will be mapped into units (grids), to associate the grids that overlap with each cell coverage area.
                                                                +Output 4 → Regular grid covering the required area, over the cells coverage +areas.

                                                              8. +
                                                              9. Distribution and aggregation: Taking into account the coverage area of the cell, users are going to be distributed, homogeneously among the grids (currently 150m x 150m or larger) associated with the cell, and the process is repeated for all cells. As we are assuming that the distribution of users in the coverage area of each cell is uniform, we are introducing an error/noise in the distribution of users by time interval, which will be transferred to population density predictions that contribute to reducing the risk of user reidentification. Each grid on the map can typically be served by several cells of different technologies and frequency bands. To obtain the number of users per grid and time interval, an aggregation is performed.
                                                                +Output 5 → Number of Users per grid, based on distribution in the cells covering that area.

                                                              10. +
                                                              11. Prediction: Based on the historical information of users by grid and interval, the prediction of users by grid and interval is made for each time interval of the future. The algorithm identifies a day of the week and time frame for which the prediction is requested. Then, it will read the records associated for the same weekday and time frame for the previous 4 weeks. +The population density forecast for next Tuesday should be similar to the one observed in the last four Tuesdays. The forecast, then, will be the average of the records of the previous 4 Tuesdays at the same time frame.
                                                                +Output 6 → Users per grid, considering historical and calendar data

                                                              12. +
                                                              13. Extrapolation: Finally, the users of the MNO mobile network are extrapolated +taking into account the market shares by geographical area (municipality) to obtain the total number of people (users or not of the mobile network with any operator).
                                                                +Output 7 → Total population per grid, considering extrapolation towards MNO market share From step 2 onwards, this is aggregated data that does not contain personal information (this is anonymous data). +
                                                              diff --git a/original/PopulationDensityData/documentation/SupportingDocuments/README.MD b/original/PopulationDensityData/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/PopulationDensityData/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/PredictiveConnectivityData/README.md b/original/PredictiveConnectivityData/README.md new file mode 100644 index 0000000000000000000000000000000000000000..cb33013d2adb678963008667ab626cf4161e03ee --- /dev/null +++ b/original/PredictiveConnectivityData/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# PredictiveConnectivityData + +Sandbox API Repository to describe, develop, document, and test the PredictiveConnectivityData Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/AQAnBw) + +## Scope + +* Service API(s) “PredictiveConnectivityData” (see APIBacklog.md) +* The API provides the capability to get the estimation of connectivity delivered by 4G/5G networks along a volume/area for a future date, time, and height. +* Use Cases: + * Network Airspace Connectivity Information for Flight Planning: Provides mobile network coverage forecasts in specific geographic areas to help identify “black volumes” and mitigate the risk of losing drone control due to poor connectivity. + * Autonomous Car Routing: Delivers mobile network coverage forecasts along the planned route of an autonomous car to support decision-making in path planning and connectivity-dependent operations. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: April 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/PredictiveConnectivityData/releases/tag/r1.2) (Fall25), with the following API versions: + * **predictive-connectivity-data v0.1.0** + [[YAML]](https://github.com/camaraproject/PredictiveConnectivityData/blob/r1.2/code/API_definitions/predictive-connectivity-data.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/PredictiveConnectivityData/r1.2/code/API_definitions/predictive-connectivity-data.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/PredictiveConnectivityData/r1.2/code/API_definitions/predictive-connectivity-data.yaml) +* The latest public release is always available here: https://github.com/camaraproject/PredictiveConnectivityData/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/PredictiveConnectivityData/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/PredictiveConnectivityData/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + +* Schedule: Monthly on Tuesdays, 10:00–11:00 UTC + (corresponds to 12:00–13:00 CEST, 06:00–07:00 EDT during Daylight Saving Time) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95479380109?password=0386fbda-1fb5-4e1a-8687-7b81fe8cacfa&invite=true) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/PAAnBw) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data.yaml b/original/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data.yaml new file mode 100644 index 0000000000000000000000000000000000000000..51ce9aea7705707c2cd90cf4856b7dbad440457e --- /dev/null +++ b/original/PredictiveConnectivityData/code/API_definitions/predictive-connectivity-data.yaml @@ -0,0 +1,1265 @@ +openapi: 3.0.3 +info: + title: Predictive Connectivity Data + description: >- + # Introduction + + With the Dynamic Predictive Connectivity Data API, the consumer can retrieve an estimation of connectivity delivered by 4/5G networks along a volume/area for a future date, time and height. + + This functionality can be used for multiple use cases, some of the possible use cases for this API are: + + - Network Airspace Connectivity Information for Drones: supporting drone flight planning with detailed analysis of mobile network coverage in the airspace across specific geographic areas. + + - Mobile Network Analysis for Autonomous Cars: enabling route planning through in-depth evaluation of mobile network availability. + + The list above is just a few examples, the API can be used for other use cases as well. + + # Relevant Definitions and concepts + + * **AGL**: Means "Above Ground Level" and describes the vertical height + above the ground. + + * **Service Level**: Describes, in measurable terms, the quality of service + a telecommunication provider furnishes a consumer within a given time period. + + * **Network Type**: Refers to the type of connectivity (4G/5G) for which to retrieve data. + + * **Signal Strength**: Raw signal strength measurements in dBm that can be optionally included in the response when supported by the implementation. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. + This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` + property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + When an asynchronous response is requested, the 202 response of the API will include an `operationId` property. This `operationId` property will + also be sent in the callback notification. The purpose of the `operationId` is to correlate an asynchronous response with its corresponding request. + + + # API Functionality + + Once a developer specifies (1) the area as a polygon shape, (2) a precision level, (3) the service + level and (4) time interval in which they want to obtain the connectivity estimation, + the API returns a data set consisting of a sequence of time ranges, with each + time range containing the input polygon subdivided into equal-sized grid cells. + + For each of the equal-sized cells of the grid, an analysis of Connectivity Levels + is reported for each time slot within the range, this includes data classified into: + + - `GC`: Means good connectivity. Service level met even in unfavorable conditions. + - `MC`: Means marginal connectivity. Service level might not be met. + - `NC`: Means no connectivity. Service level not met. + - `ND`: No connectivity data. + + Optionally, if supported by the implementation and requested by the client, raw signal strength values in dBm can also be returned for each layer. + + These values are calculated based on network data and/or prediction models trained on + such data. + + The polygon provided must comply with certain restrictions, which must be + previously validated by the developer: + + - The polygon will not exceed a certain area. + - The polygon cannot have an arbitrary complexity (unlimited number of + sides, complex shapes, etc.). + - The polygon must be associated with a location where the telco provides + mobile connectivity services. Cells outside the area supported by the + implementation will not be returned. Therefore, if a polygon is located + entirely outside the supported area, an empty array will be returned. + + The standard behaviour of the API is synchronous, although for large + area requests the API may behave asynchronously. An API invoker can enforce + asynchronous behaviour by providing a callback URL (sink) in the request, + in this case the API sends a callback to the callback URL provided with the + result of the request. If sink is included, it is RECOMMENDED for the + client to provide as well the sinkCredential property to protect the + notification endpoint. In the current version, sinkCredential.credentialType + MUST be set to ACCESSTOKEN if provided. When an asynchronous response is + requested, the 202 response of the API will include an `operationId` + property. This `operationId` property will also be sent in the callback + notification. The purpose of the `operationId` is to correlate an + asynchronous response with its corresponding request. + + ## Error handling: + + For requests with a combination of area, precision, startTime and endTime + properties involving an amount of processing that cannot be processed + synchronously, the API returns the error response + PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE. + + For requests with a combination of area, precision, startTime and endTime + properties too big for both synchronous and asynchronous processing, the API + returns the error response PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST. + + If an error happens during the asynchronous processing of the request. The + API callback will have property status with value OPERATION_NOT_COMPLETED + as an error cannot be returned in the callback. The callback will also + include the statusInfo property to add extra information about the error. + + NOTE: In case the property "Technology" is not included, the quality of connectivity + will be returned considering both 4G and 5G networks. + + # Resources and Operations overview + + The API provides one endpoint that accepts POST requests for obtaining the + connectivity in a concrete area for a concrete service level and network + type/s. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/PredictiveConnectivityData +servers: + - url: "{apiRoot}/predictive-connectivity-data/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Connectivity Data + description: Operations to retrieve connectivity information. +paths: + /retrieve: + post: + tags: + - Connectivity Data + summary: Obtain connectivity information in the specified area + description: >- + Retrieves the connectivity for a concrete area, specifying the + required service level that has to be met in the whole area in the + requested network type/s. Optionally, raw signal strength values can + be included in the response if supported by the implementation. + operationId: retrieveConnectivity + security: + - openId: + - predictive-connectivity-data:read + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/RetrieveConnectivityRequest' + examples: + RetrieveConnectivityRequestWithHeight: + summary: Request with specified height + value: + serviceLevel: C2 + area: + areaType: POLYGON + boundary: + - latitude: 50.735851 + longitude: 7.10066 + - latitude: 50.74 + longitude: 7.11 + - latitude: 50.73 + longitude: 7.12 + startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + height: 50 + RetrieveConnectivityRequestWithoutHeight: + summary: Request without specified height + value: + serviceLevel: C2 + area: + areaType: POLYGON + boundary: + - latitude: 50.735851 + longitude: 7.10066 + - latitude: 50.74 + longitude: 7.11 + - latitude: 50.73 + longitude: 7.12 + startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + required: true + responses: + '200': + description: Connectivity data result. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/ConnectivityDataResponse' + examples: + ConnectivityDataSupportedAreaResponseExample: + $ref: '#/components/examples/ConnectivityDataSupportedAreaResponseExample' + ConnectivityDataWithSignalStrengthResponseExample: + $ref: '#/components/examples/ConnectivityDataWithSignalStrengthResponseExample' + ConnectivityDataPartOfAreaNotSupportedResponseExample: + $ref: "#/components/examples/ConnectivityDataPartOfAreaNotSupportedResponseExample" + ConnectivityDataAreaNotSupportedResponseExample: + $ref: "#/components/examples/ConnectivityDataAreaNotSupportedResponseExample" + ConnectivityDataSupportedAreaResponseWithHeightExample: + $ref: '#/components/examples/ConnectivityDataSupportedAreaResponseWithHeightExample' + '202': + description: Connectivity data requested. This response is returned when the behaviour of the API is asynchronous. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/AcceptedAsyncResponse' + '400': + $ref: '#/components/responses/RetrieveConnectivityBadRequest400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '422': + $ref: '#/components/responses/RetrieveConnectivityUnprocessableContent422' + '429': + $ref: '#/components/responses/Generic429' + callbacks: + connectivityCallback: + '{$request.body#/sink}': + post: + summary: Callback for asynchronous connectivity data retrieval + description: >- + This callback is invoked to provide the result of an asynchronous + connectivity data retrieval request. + operationId: connectivityCallback + parameters: + - name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: '#/components/schemas/XCorrelator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/ConnectivityDataAsyncResponse' + examples: + ConnectivityDataSupportedAreaAsyncResponseExample: + $ref: "#/components/examples/ConnectivityDataSupportedAreaAsyncResponseExample" + ConnectivityDataOperationNotCompletedExample: + $ref: "#/components/examples/ConnectivityDataOperationNotCompletedExample" + required: true + responses: + '204': + description: Callback successfully received. + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: '{$request.body#sinkCredential.credentialType}' + headers: + x-correlator: + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RetrieveConnectivityRequest: + type: object + description: Request object for retrieving connectivity data in a specified area. + properties: + serviceLevel: + $ref: '#/components/schemas/ServiceLevel' + area: + $ref: '#/components/schemas/Area' + startTime: + type: string + format: date-time + description: >- + Start date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + endTime: + type: string + format: date-time + description: >- + End date time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + networkType: + $ref: '#/components/schemas/NetworkType' + precision: + type: integer + description: >- + Precision required of response cells. Precision defines a geohash level and corresponds to the length of the geohash for each cell. More information at [Geohash system](https://en.wikipedia.org/wiki/Geohash)" + If not included the default precision level 7 is used by default. In case of using a not supported level by the MNO, the API returns the error response `PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION`. + minimum: 1 + maximum: 12 + default: 7 + height: + description: >- + Requested prediction height in metres above ground level. + If a prediction height is specified, the response will include only the connectivity data for the layer containing that height. + If no prediction height is specified, the response will include available prediction for all heights. + type: integer + minimum: 0 + maximum: 250 + includeSignalStrength: + type: boolean + description: >- + Optional parameter to request raw signal strength values in dBm for each layer. + If set to true and supported by the implementation, the response will include + signal strength data alongside connectivity quality information. If not supported + by the implementation, this parameter will be ignored and only connectivity + quality will be returned. + default: false + sink: + type: string + format: uri + description: The address where the API response will be asynchronously delivered, using the HTTP protocol. + pattern: ^https:\/\/.+$ + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable the delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + required: + - serviceLevel + - area + - startTime + - endTime + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + POLYGON - The area is defined as a polygon. + enum: + - POLYGON + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + ServiceLevel: + description: >- + Describes the requested communication service level. Although more + categories may be added in the future, for the time being, the possible + service levels are as follows: + - C2: Command and Control. Consists in connecting an unmanned aerial vehicle with its remote controller. This link allows data transmission in both directions, facilitating real-time operation and feedback. + - STREAM_4K: Streaming in 4K quality. + - BEST_EFFORT: This service level provides a qualitative estimation of coverage based on each operator's own prediction models or public coverage maps. It does not imply any guarantee of network performance or service availability. The values of GC, MC, NC, and ND should be interpreted as approximate indicators of expected connectivity quality, not as results derived from standardised thresholds. + type: string + enum: + - C2 + - STREAM_4K + - BEST_EFFORT + NetworkType: + description: >- + Specifies the type of connectivity for which to retrieve data. Allowed + values are `4G` and `5G`. In case the property is not included, the + quality of connectivity will be returned considering both 4G and 5G + networks. + type: string + enum: + - 4G + - 5G + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + ConnectivityDataResponse: + type: object + description: >- + Response that contains information about the requested area connectivity + for the service level selected. + properties: + layerThickness: + description: Thickness in metres of each layer. + type: number + timedConnectivityData: + type: array + description: >- + Time ranges along with the connectivity data for the cells within it. + The request startTime or the request endTime have to be fully covered by the intervals. + For example, if the intervals are 1-hour long and the input date range were [2024-01-03T11:25:00Z + to 2024-01-03T12:45:00Z] it would contain 2 intervals (Interval from 2024-01-03T11:00:00Z + to 2024-01-03T12:00:00Z and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + items: + $ref: '#/components/schemas/TimedConnectivityData' + status: + $ref: '#/components/schemas/ResponseStatus' + statusInfo: + type: string + description: Information about the status, mandatory when property `status` is `OPERATION_NOT_COMPLETED` for adding extra information about the error. + example: Some error happened during the processing of the request + requestedHeight: + type: integer + description: The height in metres above ground level that was requested in the request. This property is only present if a specific height was requested. + nullable: true + example: 50 + required: + - layerThickness + - timedConnectivityData + - status + AcceptedAsyncResponse: + type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + ConnectivityDataAsyncResponse: + allOf: + - $ref: '#/components/schemas/ConnectivityDataResponse' + - type: object + properties: + operationId: + $ref: '#/components/schemas/OperationId' + required: + - operationId + OperationId: + type: string + description: The unique identifier of the asynchronous operation that is returned when the operation is initiated. + example: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ResponseStatus: + type: string + description: >- + Represents the state of the response for the input polygon defined in the request, the possible values are: + - `SUPPORTED_AREA`: The whole request area is supported. Connectivity data for the entire requested area is returned. + - `PART_OF_AREA_NOT_SUPPORTED`: Part of the requested area is outside the MNOs coverage area, the cells outside the coverage + area will have property `layerConnectivities` with all items in the array with value `ND`. + - `AREA_NOT_SUPPORTED`: The whole requested area is outside the MNOs coverage area. No data will be returned. + - `OPERATION_NOT_COMPLETED`: An error happened during asynchronous processing of the request. This status will only be returned + in case the asynchronous API behaviour is used. + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - OPERATION_NOT_COMPLETED + TimedConnectivityData: + type: object + description: >- + Represents a time interval with connectivity data for the cells in the + area. Time interval length is + determined by the implementation. The request startTime or the request + endTime have to be fully covered by the intervals. For example, if the + intervals are 1-hour long and the input date range were + [2024-01-03T11:25:00Z to 2024-01-03T12:45:00Z] it would contain 2 + intervals (Interval from 2024-01-03T11:00:00Z to 2024-01-03T12:00:00Z + and interval from 2024-01-03T12:00:00Z to 2024-01-03T13:00:00Z). + properties: + startTime: + type: string + format: date-time + description: >- + Interval start time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + example: "2023-07-03T10:00:00Z" + endTime: + type: string + format: date-time + description: >- + Interval end time. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) + and must have time zone. + example: "2023-07-03T11:00:00Z" + cellConnectivityData: + $ref: '#/components/schemas/CellConnectivityDataArray' + required: + - startTime + - endTime + - cellConnectivityData + CellConnectivityDataArray: + type: array + description: >- + Connectivity data for the different cells in a concrete time range. + items: + $ref: '#/components/schemas/CellConnectivityData' + minItems: 1 + CellConnectivityData: + description: >- + Represents a rectangular grid cell within the specified area, including + its connectivity data. + properties: + geohash: + type: string + description: >- + Coordinates of the cell represented as a string using the [Geohash + system](https://en.wikipedia.org/wiki/Geohash), encoding a + geographic location into a short string. The value length, + and thus, the cell granularity, is determined by the request body property `precision`. + example: ezdmemd + layerConnectivities: + $ref: '#/components/schemas/LayerConnectivities' + layerSignalStrengths: + $ref: '#/components/schemas/LayerSignalStrengths' + required: + - geohash + - layerConnectivities + LayerConnectivities: + type: array + minItems: 1 + description: >- + Sequence of connectivity quality values in each of the layers in which + the vertical space over the area determined by the `geohash` is + decomposed. All layers are considered having the same `layerThickness` + meters and are ordered consecutively in the array starting from the + ground (First layer will start at 0 meters AGL). So the layer at + index = N would comprise the heights, referenced to AGL, among N * + `layerThickness` meters and (N+1) * `layerThickness` meters. + If a specific height was requested, this array will contain only one element corresponding to the connectivity for the layer at that height. + + The possible connectivity values are: + - GC: Means good connectivity. Service level met even in unfavorable conditions. + - MC: Means marginal connectivity. Service level might not be met. + - NC: Means no connectivity. Service level not met. + - ND: No connectivity data. + + **NOTE**: These connectivity values are relative to the `serviceLevel` + and `networkType` specified in the request. + items: + $ref: '#/components/schemas/Connectivity' + LayerSignalStrengths: + type: array + minItems: 1 + description: >- + Predicted signal strength values in dBm for each layer. This array is optional + and will only be present if the `includeSignalStrength` parameter was set to true + in the request and is supported by the implementation. The array follows the same + structure as `layerConnectivities`, with each element corresponding to the signal + strength in dBm for the same layer index. All layers are considered having the same + `layerThickness` meters and are ordered consecutively starting from the ground + (First layer starts at 0 meters AGL). A null value indicates no signal strength + data is available for that layer. + If a specific height was requested, this array will contain only one element corresponding to the signal strength for the layer at that height. + items: + type: number + format: float + nullable: true + description: Signal strength value in dBm, or null if no data is available + example: -85.5 + Connectivity: + type: string + enum: + - GC + - MC + - NC + - ND + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + RetrieveConnectivityBadRequest400: + description: >- + Problem with the client request. In addition to regular scenario of + `INVALID_ARGUMENT`, `INVALID_CREDENTIAL`, `INVALID_TOKEN`, another scenarios may exist: + - The area is not a polygon shape or has an arbitrary complexity ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA", "message": "The area is not a polygon shape or has an arbitrary complexity") + - Indicated `startTime` is greater than the maximum allowed ("code": "PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED", "message": "Indicated startTime is greater than the maximum allowed") + - Indicated `startTime` is earlier than the minimum allowed ("code": "PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED", "message": "Indicated startTime is earlier than the minimum allowed") + - Indicated `endTime` is earlier than the `startTime` ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME", "message": "Indicated endTime is earlier than the startTime") + - Indicated time period is partially in the past and partially in the future ("code": "PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD", "message": "time period is partially in the past and partially in the future") + - Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime) ("code": "PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED", "message": "Indicated time period is greater than the maximum allowed (More than maximum hours between startTime and endTime)") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA + - PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME + - PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED + - PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD + examples: + GENERIC_400_INVALID_ARGUMENT: + value: + status: 400 + code: INVALID_ARGUMENT + message: Invalid input + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_AREA: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_AREA + message: The area is not a polygon shape or has an arbitrary complexity + PREDICTIVE_CONNECTIVITY_DATA_400_MAX_STARTTIME_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MAX_STARTTIME_EXCEEDED + message: Indicated startTime is greater than the maximum allowed + PREDICTIVE_CONNECTIVITY_DATA_400_MIN_STARTTIME_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MIN_STARTTIME_EXCEEDED + message: Indicated startTime is earlier than the minimum allowed + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_END_TIME: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_END_TIME + message: Indicated endTime is earlier than the startTime + PREDICTIVE_CONNECTIVITY_DATA_400_MAX_TIME_PERIOD_EXCEEDED: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.MAX_TIME_PERIOD_EXCEEDED + message: >- + Indicated time period is greater than the maximum allowed + (More than maximum hours between startTime and endTime) + PREDICTIVE_CONNECTIVITY_DATA_400_INVALID_TIME_PERIOD: + value: + status: 400 + code: PREDICTIVE_CONNECTIVITY_DATA.INVALID_TIME_PERIOD + message: >- + Indicated time period is partially in the past and partially in the future + RetrieveConnectivityUnprocessableContent422: + description: >- + Problem with the client request. In addition to regular scenario of + `INVALID_ARGUMENT`, another scenarios may exist: + - Indicated request is too big for both synchronous and asynchronous processing ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST", "message": "The indicated request is too big for both synchronous and asynchronous processing") + - Indicated cell precision (Geohash level) is not supported ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION", "message": "Indicated cell precision (Geohash level) is not supported") + - Indicated request is too big for synchronous processing and asynchronous processing is not enabled ("code": "PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE", "message": "The indicated request is too big for synchronous processing and asynchronous processing is not enabled") + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION + - PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE + examples: + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_REQUEST: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_REQUEST + message: >- + Indicated combination of area, time interval and precision is too big for both synchronous and + asynchronous processing + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_PRECISION: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_PRECISION + message: >- + Indicated cell precision (Geohash length) is not supported + PREDICTIVE_CONNECTIVITY_DATA_422_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 422 + code: PREDICTIVE_CONNECTIVITY_DATA.UNSUPPORTED_SYNC_RESPONSE + message: >- + Indicated combination of area, time interval and precision is too big for synchronous processing + and asynchronous processing is not enabled + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + ConnectivityDataSupportedAreaResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: SUPPORTED_AREA + ConnectivityDataPartOfAreaNotSupportedResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T13:00:00Z" + endTime: "2024-01-03T14:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: PART_OF_AREA_NOT_SUPPORTED + ConnectivityDataAreaNotSupportedResponseExample: + value: + layerThickness: 30 + timedConnectivityData: [] + status: AREA_NOT_SUPPORTED + ConnectivityDataSupportedAreaAsyncResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - startTime: "2024-01-03T12:00:00Z" + endTime: "2024-01-03T13:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + status: SUPPORTED_AREA + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ConnectivityDataOperationNotCompletedExample: + value: + layerThickness: 30 + timedConnectivityData: [] + status: OPERATION_NOT_COMPLETED + statusInfo: Some error happened during the processing of the request + operationId: 2322f362-eaab-4cf3-86d2-efcbdf3a7cb4 + ConnectivityDataWithSignalStrengthResponseExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + layerSignalStrengths: + - -85.5 + - -84.0 + - -83.0 + - -82.0 + - -81.0 + - null + - null + - null + - geohash: ezdmemc + layerConnectivities: + - GC + - GC + - GC + - GC + - GC + - NC + - NC + - NC + layerSignalStrengths: + - -85.5 + - -84.0 + - -83.0 + - -82.0 + - -81.0 + - -81.5 + - -81.0 + - -85.0 + status: SUPPORTED_AREA + ConnectivityDataSupportedAreaResponseWithHeightExample: + value: + layerThickness: 30 + timedConnectivityData: + - startTime: "2024-01-03T11:00:00Z" + endTime: "2024-01-03T12:00:00Z" + cellConnectivityData: + - geohash: ezdmemd + layerConnectivities: + - GC + - geohash: ezdmemc + layerConnectivities: + - GC + status: SUPPORTED_AREA + requestedHeight: 50 diff --git a/original/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.md b/original/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..39155d9944fc4aaade333e300deae151e973d64e --- /dev/null +++ b/original/PredictiveConnectivityData/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.md @@ -0,0 +1,12 @@ +# PredictiveConnectivityData API User Story + +| **Item** | **Details** | +|---------|-------------| +| **_Summary_** | The API provides the capability to get the estimation of connectivity delivered by 4G/5G networks along a volume/area for a future date, time and height. | +| **_Actors and Scope_** | **Scope:**
                                                              - Retrieve predicted mobile connectivity (4G/5G) for a defined polygonal area, time interval, and height.
                                                              - Supports planning in aerial and terrestrial domains.

                                                              **Use Case 1 – Network Airspace Connectivity Information (forecast) for Flight Planning:**
                                                              - Delivers comprehensive analysis with data about mobile network coverage in specific geographic areas.
                                                              - Identifies “black volumes” to avoid drone disconnection risks.

                                                              **Use Case 2 – Autonomous Car:**
                                                              - Provides predicted mobile network coverage data along the vehicle route. | +| **_Pre-conditions_** | – The client must provide the following inputs:
                                                              1. **Requested Area:** polygonal area defined by coordinates forming a closed loop (Required)
                                                              2. **Start Time** future controlled time of departure (Required). **End Time:** future controlled time of arrival (Required).
                                                              3. **Service Level:** type of service needed (e.g., C2, STREAM_4K) (Required)
                                                              4. **Technology:** 4G or 5G (Optional)
                                                              5. **Height** and **Precision** (as suggested in scope evolution discussions) | +| **_Activities/Steps_** | - The client submits a request including the inputs listed above.
                                                              - The API responds with:
                                                              1. An array of cells (Geohash-encoded) with hourly connectivity predictions:
                                                                  - GC: Good Connectivity
                                                                  - MC: Marginal Connectivity
                                                                  - NC: No Connectivity
                                                              2. Layer thickness in meters (AGL)
                                                              – Output may optionally include **Signal Strength** instead of **Service Level**. | +| **_Post-conditions_** | The requester obtains connectivity forecasts that support planning for flight or vehicle route safety based on mobile network availability. | +| **_Exceptions_** | Several exceptions might occur during the PredictiveConnectivityData API operations:
                                                              - **Invalid input:** Required fields missing or incorrectly formatted (e.g., malformed polygon, missing Start/End Time or Service Level).
                                                              - **Unsupported values:** Inputs that exceed defined limits (e.g., time window too far in the future, unsupported technology type).
                                                              - **Unavailable data:** The requested area, time, or combination of parameters does not match any available prediction dataset. | + + diff --git a/original/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist.md b/original/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..cd267375f0307b4dad9286651323ee0b56dd9f03 --- /dev/null +++ b/original/PredictiveConnectivityData/documentation/API_documentation/predictive-connectivity-data-API-Readiness-Checklist.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for predictive-connectivity-data v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                              public | stable
                                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/predictive-connectivity-data.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3)*** | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0 | +| 5 | API documentation | M | M | M | M | Y | [inline in YAML](/code/API_definitions/predictive-connectivity-data.yaml) | +| 6 | User stories | O | O | O | M | N | [link](/documentation/API_documentation/Predictive-Connectivity-Data_User_Story.mdd) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/predictive-connectivity-data.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/predictive-connectivity-data.feature) | +| 9 | Test result statement | O | O | O | M | N | TBC | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.2 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | No | +| 13 | API description (for marketing) | O | O | M | M | Y | [Wiki link](https://lf-camaraproject.atlassian.net/wiki/x/owAjBw) | + +*** *The asynchronous response currently does not follow the CloudEvents delivery format as required by Commonalities r3.3. See Issue [#38](https://github.com/camaraproject/PredictiveConnectivityData/issues/38). This will be addressed post-Fall’25 and released as v0.2.0 to ensure full compliance* + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/QoSBooking/README.md b/original/QoSBooking/README.md new file mode 100644 index 0000000000000000000000000000000000000000..a56661b39778ea9f56b3532d777eebf5edfa190c --- /dev/null +++ b/original/QoSBooking/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# QoSBooking + +Sandbox API Repository to describe, develop, document, and test the QoSBooking Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/SADHB) + +## Scope + +* Service API(s) “QoSBooking” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * book an assignment of a certain QoS Profile to a certain device with some conditions such as start time, duration and location in advance. + * update the booking, remove it, and get the information of it. +* Describe, develop, document, and test the API(s) +* Started: January 2025 + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/QoSBooking/releases/tag/r1.2) (Fall25), with the following API versions: + * **qos-booking-and-assignment v0.1.0** + [[YAML]](https://github.com/camaraproject/QoSBooking/blob/r1.2/code/API_definitions/qos-booking-and-assignment.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking-and-assignment.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking-and-assignment.yaml) + * **qos-booking v0.1.0** + [[YAML]](https://github.com/camaraproject/QoSBooking/blob/r1.2/code/API_definitions/qos-booking.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QoSBooking/r1.2/code/API_definitions/qos-booking.yaml) +* The latest public release is always available here: https://github.com/camaraproject/QoSBooking/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/QoSBooking/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/QoSBooking/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly on Friday at 13:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94112812156?password=f238d6af-c959-48d7-a862-abdb3c648e40) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/ABje) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/QoSBooking/code/API_definitions/qos-booking-and-assignment.yaml b/original/QoSBooking/code/API_definitions/qos-booking-and-assignment.yaml new file mode 100644 index 0000000000000000000000000000000000000000..d85f6a34f11d097d81f5ce82c41f8189cce1f92e --- /dev/null +++ b/original/QoSBooking/code/API_definitions/qos-booking-and-assignment.yaml @@ -0,0 +1,2099 @@ +openapi: 3.0.3 +info: + title: QoS Booking and Assignment + description: | + This API enables API consumers to request, in advance, certain network performance to be provided by Telco networks, without having in-depth knowledge of the underlying network complexities (e.g. the 4G/5G system in case of a mobile network) for a number of devices, at a given location, for a period of time. + + The API enables API consumers to book a specific QoS profile for one or more devices with conditions such as the start time, duration and location. Once the booking is confirmed the enduser can assign devices to the booking. + The network operator will provision and activate those devices with the required and agreed network quality at the given time and conditions + + # Relevant terms and definitions + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the network operator for the device, at the request time. After the booking request is accepted, the device may get different IP addresses, but the booking will still apply to the device that was identified during the request process. Note: Network Access Identifier is defined for future use and will not be supported with v0.1 of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (e.g. duration expiration) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # Resources and Operations overview + The API defines seven major operations in two groups: + + Booking: + + - An operation to setup a new QoS Booking for one or more devices. + - An operation to get the information about an existing QoS Booking, identified by its `BookingId`. + - An operation to terminate an existing QoS Booking, identified by its `BookingId`. + + Device Assignment: + + - An operation to assign one or more devices to the existing booking identified by its `BookingId`. + - An operation to release one or more devices from the booking identified by its `BookingId`. + - An operation to get all the devices assigned to a given booking identified by its `BookingId`. + - An operation to get all the associated QoS Booking for a given device. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` or `devices` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. In this case, only one device can be provided at a time. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS booking in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QoSBooking + +servers: + - url: "{apiRoot}/qos-booking-and-assignment/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: QoS Booking + description: Book and manage QoS for multiple devices in advance + - name: Device Assignment + description: Manage the assignment of devices for a given QoS Booking + +paths: + /qos-bookings: + post: + tags: + - QoS Booking + summary: This operation reserves required QoS in advance up to a certain number of devices in certain serviceArea and time slot. The devices have to be attached with a subsequent operation. + description: | + This operation reserves a Quality of Service (QoS) booking for a specified number of devices, service area, and scheduled time/duration. + Devices can be assigned to the booking at any time after the reservation is successful and before the scheduled end-time. + - `Pre-assigned devices :` These devices will be automatically provisioned and activated with the requested QoS profile exactly when the scheduled start time arrives. + - `Late-assigned devices:` Devices assigned after the schedule starts (but before it ends) will be provisioned and activated with the requested QoS profile immediately upon assignment. + This operation will return with the following responses: + - `HTTP 201 (status: SUCCESSFUL):` The operator was able to confirm the booking immediately. + - `HTTP 202 (status: PENDING). :` The operator is unable to confirm immediately, and the booking status is pending. A subsequent notification will be sent to confirm the final status, if available. + - `HTTP 4xx (Failure Condition) :` The operator determined that the booking is unavailable. The response will include specific status codes and descriptions detailing the error. + - Respective `statusInfo` contains additional information under certain conditions. + operationId: createBooking + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Input Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInput" + examples: + BOOKING_INPUT_1: + $ref: "#/components/examples/BOOKING_INPUT_1" + BOOKING_INPUT_2: + $ref: "#/components/examples/BOOKING_INPUT_2" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Booking notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Booking change related event occurs. + operationId: postBookingNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Booking creation is successful. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_SUCCESSFUL: + $ref: "#/components/examples/BOOKING_SUCCESSFUL" + "202": + description: | + Booking request is accepted but pending. + Confirmation of success or failure will be sent as a callback notification. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_PENDING: + $ref: "#/components/examples/BOOKING_PENDING" + "400": + $ref: "#/components/responses/CreateBookingOrAssign400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:create" + + /qos-bookings/{bookingId}: + get: + tags: + - QoS Booking + summary: Get the Booking information for a given QoS Booking identified by `bookingId`. + description: | + This operation is synchronous and retrieves the details of an existing Quality of Service (QoS) booking using its unique identifier (`bookingId`). This `bookingId` is the identifier returned by the initial booking operation upon successful creation. + Response Scenarios: + - `HTTP 200 (status: SUCCESSFUL):` The booking details are successfully retrieved and returned in the response body along with the remaining number of devices still can be assigned to the booking. + - `HTTP 4xx (Failure Condition) :` The request failed, and an appropriate HTTP 4xx error code is returned with a specific status and description. + operationId: getBookingById + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_RETRIEVED: + $ref: "#/components/examples/BOOKING_RETRIEVED" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:read" + + delete: + tags: + - QoS Booking + summary: This operation cancels an existing QoS Booking and release the associated resources. + description: | + This operation cancels and deletes a specific QoS booking using its unique identifier and releases the resources related to that booking. It supports both synchronous and asynchronous processing. + Constraints & Notes: + - The Quality of Service (QoS) booking must have been created by the same API client identified in the access token. + - The SUCCESSFUL and FAILURE conditions for a deletion are dependent on the operator's specific implementation. + - Operators SHOULD properly document their `Booking Cancellation` behavior with clear policies and the respective terms and conditions. + Response Scenarios: + - `HTTP 200 (status: SUCCESSFUL):` The booking was deleted immediately (synchronous success). + - `HTTP 202 (status: PENDING). :` The request has been accepted for processing, but the deletion is not yet complete (asynchronous processing). A subsequent notification will be sent to confirm the final status. + - `HTTP 4xx (Failure Condition) :` The request failed, and an appropriate HTTP 4xx error code is returned with a specific status and description. + operationId: deleteBooking + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Booking deleted. `status` in the response will be `SUCCESSFUL` and `statusInfo` will be `BOOKING_CANCELLED` + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + BOOKING_CANCELLED: + $ref: "#/components/examples/BOOKING_CANCELLED" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `PENDING` and `statusInfo` will be `DELETE_REQUESTED` + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingOutput" + examples: + CANCELLATION_PENDING: + $ref: "#/components/examples/CANCELLATION_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:delete" + + /qos-bookings/{bookingId}/devices/assign: + post: + tags: + - Device Assignment + summary: Assign one or more devices to an existing QoS Booking identified by `bookingId` + description: | + This endpoint allows the end user to assign one or more devices to the existing QoS Booking. + - If the assignment is successful for all the devices, the call will return 201 success code with status `SUCCESSFUL` and the network is available for the said devices to connect and use them at the requested time + - If the assignment request failed for some reason, this call we be retured with 4xx error code with appropirate status codes + - This is an asynchronous call, and status = `PENDING` if the network is still working on your request. A callback will come with appropriate status. + - If the network could not assign all the requested devices, then status = `PARTIAL_SUCCESS` and the `statusInfo` will have additional information. + - If a 2-legged access token is used, then the device details SHOULD BE provided as part of the input, and the output will return the array of actually assigned devices. + - If a 3-legged access token is used, then the device information are identified from the access token, so only one device is implicitly assigned, and the return value may not contain the assigned device information + operationId: assignDevices + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInput" + examples: + ASSIGNMENT_INPUT_1: + $ref: "#/components/examples/ASSIGNMENT_INPUT_1" + ASSIGNMENT_INPUT_2: + $ref: "#/components/examples/ASSIGNMENT_INPUT_2" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Assignment notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Assignment change related event occurs. + operationId: postAssignmentNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: At least one device is assigned to the booking. The developer can call this endpoint multiple times with appropriate information + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_SUCCESSFUL: + $ref: "#/components/examples/ASSIGNMENT_SUCCESSFUL" + ASSIGNMENT_PARTIAL_SUCCESS: + $ref: "#/components/examples/ASSIGNMENT_PARTIAL_SUCCESS" + ASSIGNMENT_FAILURE_1: + $ref: "#/components/examples/ASSIGNMENT_FAILURE_1" + ASSIGNMENT_FAILURE_2: + $ref: "#/components/examples/ASSIGNMENT_FAILURE_2" + + "202": + description: | + Assignment request is accepted but pending decision. + Once the decision is made a callback notification will be sent with appropirate success or failure Confirmation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_PENDING: + $ref: "#/components/examples/ASSIGNMENT_PENDING" + + "400": + $ref: "#/components/responses/CreateBookingOrAssign400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:create" + + /qos-bookings/{bookingId}/devices: + get: + tags: + - Device Assignment + summary: Get the list of devices assigned to an existing QoS Booking + description: | + This endpoint allows the end user to retrieve the list of devices assigned to the existing QoS Booking. + - status = `SUCCESSFUL` if the operation is successful + - status = `FAILURE` if the operation is unsuccessful then the `statusInfo` will have more information. + - GET may not return the identifying details of all the devices assigned to the booking. There are certain situations, identifying details of certain devices can't be disclosed because of privacy laws, jurisdiction restrictions, and some legal requirements. + In such a situation the operator SHOULD properly communicate this to the API consumer that device identifiers of certain devices are not disclosed. `statusInfo` = `DEVICE_DISCLOSURE_POLICY_APPLIED` + - The API consumer can determine; how many devices are actually in the booking from 'bookingDetails'; but may not know the identifying details of all those devices. + - A classic example is: Some of the devices are assigned using a 3-legged access token; Or a booking is made in one jurisdiction and the actual usage is happening in another jurisdiction which has several privacy restrictions. + + operationId: getDevicesByBookingId + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: List of all devices assigned to the booking is returned. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RETRIEVED_1: + $ref: "#/components/examples/ASSIGNMENT_RETRIEVED_1" + ASSIGNMENT_RETRIEVED_2: + $ref: "#/components/examples/ASSIGNMENT_RETRIEVED_2" + + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:read" + + /qos-bookings/{bookingId}/devices/release: + post: + tags: + - Device Assignment + summary: Release one or more devices from the given QoS Booking + description: | + This endpoint will release one or more assigned devices. The timing of the release depends on the current status: + + - `Before the scheduled time:` The release will be mostly immediate. + - `After the scheduled time (devices active):` The release may take time as the system needs to free up associated resources. + + A callback notification will be sent once the devices are successfully released, provided one is registered with the device assignment. This endpoint functions in both synchronous and asynchronous modes. + - If the device is assigned using 3-legged access token: + - If the device is active, then release can happen in the same way. + - If the device has failed for some reason, and the device information is not known, then the device can't be released from booking. + - This call uses the POST method to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via DELETE. + operationId: releaseDevices + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to release devices + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentInput" + examples: + ASSIGNMENT_RELEASE_INPUT: + $ref: "#/components/examples/ASSIGNMENT_RELEASE_INPUT" + required: true + responses: + "200": + description: | + At least one of the requested devices has been successfully released from the booking. + + Example: + + If an end-user requests to release two devices but the network can release only one: + - The `status` will be `PARTIAL_SUCCESS`. + - The `statusInfo` field will contain additional details. + + The returned message body will also contain the list of the actual devices that were released. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RELEASED: + $ref: "#/components/examples/ASSIGNMENT_RELEASED" + "202": + description: | + The release request is accepted but is pending for internal reasons, or the release process has started and is currently in progress. + Once all devices are released, a callback notification will be sent with the appropriate success or failure confirmation + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/DeviceAssignmentOutput" + examples: + ASSIGNMENT_RELEASE_PENDING: + $ref: "#/components/examples/ASSIGNMENT_RELEASE_PENDING" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:devices:delete" + + /qos-bookings/retrieve: + post: + tags: + - Device Assignment + summary: Retrieves all the bookings that corresponds to a device + description: | + Querying for QoS Booking resource information details for a device. + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The QoS Booking must have been created by the same API client given in the access token. + - If no QoS booking is found for the requested device, an empty array is returned. + - This call uses the POST method to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + operationId: retrieveBookingByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve a booking by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingByDevice" + examples: + RETRIEVE_BOOKINGS_INPUT: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_INPUT" + required: true + responses: + "200": + description: Returns the QoS booking information for a given device. A device may have multiple bookings (for several times and locations), thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingsOutput" + examples: + RETRIEVE_BOOKINGS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_ONE_ITEM" + RETRIEVE_BOOKINGS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_NO_ITEMS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking-and-assignment:qos-bookings:retrieve-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + BookingId: + name: bookingId + in: path + description: Booking ID that was obtained from the createBooking operation + required: true + schema: + $ref: "#/components/schemas/BookingId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + BookingId: + description: Booking Identifier in UUID format + type: string + format: uuid + + BookingInput: + description: | + Basic input that are required to book QoS in advance. `numDevices` represents the maximum number of devices the enduser wants the operator to reserve in advance. + allOf: + - type: object + properties: + numDevices: + $ref: "#/components/schemas/DeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + sink: + type: string + format: uri + pattern: "^https:\/\/.+$" + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + - startTime + - duration + - serviceArea + + BookingDetails: + description: | + The details of booking. This schema can be used in any place booking details need to be returned. + + allOf: + - type: object + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + totalDevices: + $ref: "#/components/schemas/DeviceCount" + remainingDevices: + $ref: "#/components/schemas/RemainingDeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + required: + - bookingId + - remainingDevices + - qosProfile + - startTime + - duration + - serviceArea + + BookingOutput: + description: | + - If the booking endpoint returns synchronously, `BookingOutput` will be part of the return message body. For async success a follow-up `get` endpoint will return the details of the actual booking. + - It returns original number of devices that are requested as well as the remaining number of devices in the booking that can be assigned + `remainingDevices` >= 0 and <= `totalDevices` + - Once a device is successfully assigned to the booking, `remainingDevices` will be reduced by 1, and once the device is released then it will be incremented by 1 + - Booking Information is also returned as part of the message body when the devices are successfully assigned to the booking. + - `bookingId` may not be present if the booking was not successful + + allOf: + - type: object + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + totalDevices: + $ref: "#/components/schemas/DeviceCount" + remainingDevices: + $ref: "#/components/schemas/RemainingDeviceCount" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + startTime: + $ref: "#/components/schemas/Time" + duration: + $ref: "#/components/schemas/Duration" + serviceArea: + $ref: "#/components/schemas/Area" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/BookingStatusInfo" + required: + - remainingDevices + - qosProfile + - startTime + - duration + - serviceArea + - status + + DeviceAssignmentInput: + description: | + Array of devices that needs to be assigned to a booking. + - The size of the array should be less than or equal to the devices that are remaining in the original booking. + - At least one device identifier is required when a 2-legged access token is used. + - In a 3-legged situation, only one device can be assigned at a time, and the device details are automatically generated from the access token + - In such a situation, `Devices` array SHOULD NOT be provided. + type: object + properties: + devices: + $ref: "#/components/schemas/Devices" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + + DeviceAssignmentOutput: + description: | + This schema is used to return device information associated with the booking as an output. + - It will have the `bookingDetails` along with all the originally requested information. + - In some situations (ex: assignments using 3-legged access token) the device details should not be disclosed as per the privacy and other legal requirements. + - For example: + - If there are 10 devices assigned in a booking; but the GET operation returns only 7; It means 3 devices can't be disclosed + - The source of truth is in the following properties in the booking details: `totalDevices` and `remainingDevices`. + - In such a situation the operator SHOULD set `statusInfo` as `DEVICE_DISCLOSURE_POLICY_APPLIED` to clearly communicate the fact that some devices are not disclosed. + + allOf: + - type: object + properties: + bookingDetails: + $ref: "#/components/schemas/BookingDetails" + devices: + $ref: "#/components/schemas/DeviceResponseArray" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - status + + RetrieveBookingByDevice: + description: Attributes to look for QoS Booking + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveBookingsOutput: + description: QoS bookings for a given device + type: array + items: + $ref: "#/components/schemas/BookingDetails" + minItems: 0 + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the [QoS Profile API](link TBC). + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-booking-and-assignment.v0.status-changed" + - "org.camaraproject.qos-booking-and-assignment.v0.assignment-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-booking-and-assignment.v0.status-changed: "#/components/schemas/EventBookingStatusChanged" + org.camaraproject.qos-booking-and-assignment.v0.assignment-status-changed: "#/components/schemas/EventAssignmentStatusChanged" + + + EventBookingStatusChanged: + description: Event to notify a QoS Booking status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - bookingDetails + - status + properties: + bookingDetails: + $ref: "#/components/schemas/BookingOutput" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/BookingStatusInfo" + required: + - data + + EventAssignmentStatusChanged: + description: Event to notify a Device Assignment status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - status + - deviceDetails + properties: + deviceDetails: + $ref: "#/components/schemas/DeviceAssignmentOutput" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/AssignmentStatusInfo" + required: + - data + + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Time: + description: | + Date and time when the API consumer requests the QoS profile to become available. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:31Z" + + Duration: + description: | + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). + Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + The actual value may be limited by QoS Profile. + type: integer + format: int32 + minimum: 1 + example: 3600 + + Devices: + description: | + Array of devices to be assigned to the booking and provisioned. At least one device is required. + Not to be provided when a 3-legged access token already identifies a device. + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Device" + + DeviceResponseArray: + description: List of device identifiers that have been successfully assigned based on the request. + type: array + minItems: 1 + items: + $ref: "#/components/schemas/DeviceResponse" + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Status: + description: | + The current status of the requests in any of the endpoints in Booking or Assignment. The status can be one of the following: + * `PENDING` - The request is still being processed. For booking, booking is requested and for assignments, the request is pending. 'statusInfo' may have additional information. + * `SUCCESSFUL` - The request is processed successfully. This may happen immediately. The state will go to PENDING and then back to SUCCESSFUL in certain conditions. + * `PARTIAL_SUCCESS` - The request is processed with partial success - applicable to device assignments. `statusInfo` may have additional information. This enum is optional, and useful if the operator wants to communicate partial success. + * `FAILURE` - The request has been processed but failed. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - PENDING + - SUCCESSFUL + - PARTIAL_SUCCESS + - FAILURE + + StatusChanged: + description: | + The current status of PENDING can be changed to SUCCESSFUL or PARTIAL_SUCCESS or FAILURE. + In some situations (rare situations) a SUCCESSFUL booking or a device assignment may turn into a FAILURE because of natural disasters, catastrophic events, or for a unknown reason. + In such a situations 'statusInfo' may provide additional information about the reason for the unavailability + type: string + enum: + - SUCCESSFUL + - PARTIAL_SUCCESS + - FAILURE + + BookingStatusInfo: + description: | + This schema provides a detailed status of a booking request + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the QoS Booking for unknown reasons + * `DELETE_REQUESTED`- User requested the deletion of the QoS Booking + * `VALIDATION_PENDING` - The validation is pending. The end user will get a callback with the availability of the booking + * `SERVICE_NOT_AVAILABLE` - The requested booking could not be fulfilled because of operator could not support the service area/number of devices/qosProfile in the requested time + * `QOS_PROFILE_NOT_SUPPORTED` - The requested QoS Profile is not supported by the operator + * `BOOKING_UNKNOWN_ERROR` - An unknown error happened while booking + * `BOOKING_ACCEPTED` - The requested booking is completed successfully. + * `BOOKING_CANCELLED` - The given bookingId was cancelled by the user and is no more valid. + * `BOOKING_EXPIRED` - Booking schedule ended, and the given bookingId is expired and is no more valid + * `BOOKING_ACTIVATED` - Booking schedule started and the booking is activated. + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + - VALIDATION_PENDING + - SERVICE_NOT_AVAILABLE + - QOS_PROFILE_NOT_SUPPORTED + - BOOKING_UNKNOWN_ERROR + - BOOKING_ACCEPTED + - BOOKING_CANCELLED + - BOOKING_EXPIRED + - BOOKING_ACTIVATED + + AssignmentStatusInfo: + description: | + This schema provides a detailed status of an assignment request + * `DEVICE_NOT_FOUND` - One or some of the devices are not found to validate and associate to booking. + * `DEVICE_UNKNOWN_ERROR` - One, or more, or all of devices are not assigned or not released because of unknown error. + * `DEVICE_DISCLOSURE_POLICY_APPLIED` - Some or all of the devices are not disclosed because of privacy, or legal requirements, or for unknown reasons. + * `QUOTA_EXCEEDED` - The number of devices requested to assign to a booking is more than the allocated total for the booking. Only remaining devices are assigned + * `VALIDATION_PENDING` - The device assignment request is pending for validation and verification + * `ASSIGNMENT_COMPLETED` - The request assignment of devices is successfully completed + * `BOOKING_INVALID` - The user requests to release a device from booking, but the booking is invalid + * `BOOKING_CANCELLED` - The user requests to release a device from booking, but the booking is cancelled + * `BOOKING_EXPIRED` - The user requests to release a device from booking, but the booking is expired and no more active + * `BOOKING_TERMINATED` - For unknown reasons booking is terminated by the operator. A booking callback may be issued. + * `RELEASE_PENDING` - Release of requested devices is currently in progress. Some might have already been released, and some are still being processed. + + type: string + enum: + - DEVICE_NOT_FOUND + - DEVICE_UNKNOWN_ERROR + - DEVICE_DISCLOSURE_POLICY_APPLIED + - QUOTA_EXCEEDED + - VALIDATION_PENDING + - ASSIGNMENT_COMPLETED + - BOOKING_INVALID + - BOOKING_CANCELLED + - BOOKING_EXPIRED + - BOOKING_TERMINATED + - RELEASE_PENDING + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + DeviceCount: + description: | + Number of devices that may be assigned to the booking. + type: integer + default: 1 + + RemainingDeviceCount: + description: | + Number of devices that are remaining in the current booking. + type: integer + minimum: 0 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateBookingOrAssign400: + description: Bad Request when creating a QoS booking or assigning devices to a booking. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QOS_BOOKING.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QOS_BOOKING.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + BookingConflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing booking for the same device. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + BOOKING_INPUT_1: + summary: Booking Request Example-1 + description: This is an example of a booking request. + value: + numDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + BOOKING_INPUT_2: + summary: Booking Request Example-2 + description: This is an example of a booking request. + value: + numDevices: 27 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "POLYGON" + boundary: + [ + [-122.406558, 37.789172], + [-122.396558, 37.789172], + [-122.396558, 37.779172], + [-122.406558, 37.779172] + ] + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + + BOOKING_SUCCESSFUL: + summary: Booking Successful + description: QoS Booking is successful and valid `bookingId` is returned along with other input parameters. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACCEPTED" + + BOOKING_FAILURE: + summary: Booking Failed + description: QoS Booking failed, `statusInfo` has additional info. No `bookingId` will be returned. + value: + totalDevices: 0 + remainingDevices: 0 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "FAILURE" + statusInfo: "SERVICE_NOT_AVAILABLE" + + BOOKING_PENDING: + summary: Booking Pending + description: QoS Booking request is pending, `statusInfo` has additional info. No `bookingId` will be returned. + value: + totalDevices: 0 + remainingDevices: 0 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + + BOOKING_RETRIEVED: + summary: Retrieve Booking + description: Retrieve booking information from its `bookingId`. `statusInfo` will provide the current status of the booking. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACTIVATED" + + BOOKING_CANCELLED: + summary: Cancel an existing booking + description: Delete a booking using a valid `bookingId`. Delete operation is successful. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_CANCELLED" + + CANCELLATION_PENDING: + summary: Cancellation is Requested + description: Delete a booking using a valid `bookingId`. Delete operation is pending as operator may need more time to process the request. + value: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 7 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "DELETE_REQUESTED" + + ASSIGNMENT_INPUT_1: + summary: Assignment Input - All Identifiers + description: Assignment Input example. To demonstrate, four devices are used, each with a different type of device identifiers. + value: + devices: + - phoneNumber: "+14145550101" + - networkAccessIdentifier: "+123456789@domain.com" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + - ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + ASSIGNMENT_INPUT_2: + summary: Assignment Input - Phone Number only + description: Assignment Input example. To demonstrate, two devices are used, each device is identified with a phone number. + value: + devices: + - phoneNumber: "+14145550101" + - phoneNumber: "+14145550202" + sink: "https://application-server.com/notifications" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "" + accessTokenExpiresUtc: "2025-12-31T23:59:59Z" + accessTokenType: bearer + + ASSIGNMENT_SUCCESSFUL: + summary: Assignment Successful + description: Assignment is successful and all requested devices were successfully assigned to the given booking. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 11 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - networkAccessIdentifier: "+123456789@domain.com" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + - ipv6Address: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_PARTIAL_SUCCESS: + summary: Assignment Partially Successful + description: Assignment is successful and some but not all of the requested devices are assigned. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + status: "PARTIAL_SUCCESS" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_PENDING: + summary: Assignment Pending + description: Assignment request is still being processed. None of the requested devices are assigned. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "PENDING" + statusInfo: "VALIDATION_PENDING" + + ASSIGNMENT_FAILURE_1: + summary: Assignment Failed + description: Assignment request failed. Booking is still valid. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 15 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "FAILURE" + statusInfo: "QUOTA_EXCEEDED" + + ASSIGNMENT_FAILURE_2: + summary: Assignment Failed for unknown booking information + description: Assignment request failed. Provided `bookingId` is correctly formed but not available. In such a situation, value contains only `status` and `statusInfo`. + value: + status: "FAILURE" + statusInfo: "BOOKING_INVALID" + + ASSIGNMENT_RELEASE_INPUT: + summary: Assignment Release Input + description: This is an example of a device that needs to be released from the given booking. + value: + devices: + - phoneNumber: "+14145550101" + + ASSIGNMENT_RELEASED: + summary: Assignment released successfully + description: Assignment is cancelled successfully and the requested devices are released from booking. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 14 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_RELEASE_PENDING: + summary: Release is pending for requested devices + description: Release of requested devices is currently in progress. Some might have already been released, and some are still being processed. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 14 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + status: "PENDING" + statusInfo: "RELEASE_PENDING" + + ASSIGNMENT_RETRIEVED_1: + summary: Retrieve successful + description: Successfully retrieved assigned devices. All devices are visible in this particular case. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + devices: + - phoneNumber: "+14145550101" + - phoneNumber: "+14145550202" + status: "SUCCESSFUL" + statusInfo: "ASSIGNMENT_COMPLETED" + + ASSIGNMENT_RETRIEVED_2: + summary: Retrieve successful - No device details + description: Successfully retrieved assigned devices. Device details are not visible because of policy restrictions. + value: + bookingDetails: + bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "DEVICE_DISCLOSURE_POLICY_APPLIED" + + RETRIEVE_BOOKINGS_INPUT: + summary: Input to Retrieve Bookings + description: This is an example of a device that is given as input to Retrieve Bookings + value: + device: + phoneNumber: "+14145550101" + + RETRIEVE_BOOKINGS_ONE_ITEM: + summary: Retrieve successful + description: Successfully retrieved assigned bookings for a given device. The device is part of only one booking. + value: + - bookingId: "8e2f6f30-0a1c-4c6b-92e1-1bd05aef1c58" + totalDevices: 15 + remainingDevices: 13 + qosProfile: "QOS_MEDIA_BROADCAST" + startTime: "2025-10-27T15:00:00.000Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 37.735851 + longitude: -127.10066 + radius: 100 + status: "SUCCESSFUL" + statusInfo: "BOOKING_ACCEPTED" + + RETRIEVE_BOOKINGS_NO_ITEMS: + summary: No bookings found for the device + description: No bookings are found for the device, value contains only empty array + value: [] diff --git a/original/QoSBooking/code/API_definitions/qos-booking.yaml b/original/QoSBooking/code/API_definitions/qos-booking.yaml new file mode 100644 index 0000000000000000000000000000000000000000..21b0709f8049bc897e6b7cbdfea1c773e7178e9e --- /dev/null +++ b/original/QoSBooking/code/API_definitions/qos-booking.yaml @@ -0,0 +1,1488 @@ +openapi: 3.0.3 +info: + title: QoS Booking + description: | + The QoS (Quality of Service) Booking API provides programmable interface for developers and other users (capabilities consumers) to request in advance certain network conditions to be provided by Telco networks, without the necessity to have an in-depth knowledge of the underlying network complexity (e.g. the 4G/5G system in case of a mobile network). + + The API enables API consumers to book the assignment of a predefined QoS profile to a specific device, with some conditions such as the start time, duration and location. + + + # Relevant terms and definitions + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone number, or Network Access Identifier assigned by the network operator for the device, at the request time. After the booking request is accepted, the device may get different IP addresses, but the booking will still apply to the device that was identified during the request process. Note: Network Access Identifier is defined for future use and will not be supported with v0.1 of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (e.g. duration expiration) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # Resources and Operations overview + The API defines four operations: + + - An operation to setup a new QoS Booking for a given device. + - An operation to get the information about a specific QoS Booking, identified by its `BookingId`. + - An operation to get the QoS Booking for a given device. + - An operation to terminate a QoS Booking, identified by its `BookingId`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS booking in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: tbd + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/QoSBooking + +servers: + - url: "{apiRoot}/qos-booking/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: Device QoS Booking + description: Manage the booking of QoS + +paths: + /device-qos-bookings: + post: + tags: + - Device QoS Booking + summary: Sets a new booking of QoS for a device + description: | + Triggers a new booking to assign certain QoS Profile to certain device. + + - If the booking is completed synchronously, the response will be 201 with `status` = `SCHEDULED`. + - If the booking request is accepted but not yet completed, the response will be 201 with `status` = `REQUESTED`. + - If the operator determines synchronously that the booking request cannot be fulfilled, the response will be 201 with `status` = `UNAVAILABLE`. + + - If the request includes a notification callback, the client will receive a `status-changed` event with the outcome of the process. The event will be sent also for synchronous operations. + + **NOTES:** + - When the booking status becomes `UNAVAILABLE`, the QoS Booking resource is not immediately released, but will get deleted automatically, at earliest 360 seconds after. + + This behavior allows clients which are not receiving notification events but are polling, to get the booking status information. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createBooking + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new booking + content: + application/json: + schema: + $ref: "#/components/schemas/CreateBooking" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Booking notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS Booking change related event occurs. + Currently only `BOOKING_STATUS_CHANGED` event is defined. + operationId: postBookingNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + BOOKING_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/BOOKING_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Booking created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE" + BOOKING_UNAVAILABLE: + $ref: "#/components/examples/BOOKING_UNAVAILABLE" + "400": + $ref: "#/components/responses/CreateBooking400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/BookingConflict409" + "422": + $ref: "#/components/responses/BookingUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:create" + + /device-qos-bookings/{bookingId}: + get: + tags: + - Device QoS Booking + summary: Get QoS Booking information + description: | + Querying for QoS Booking information details + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. + - The QoS Booking must have been created by the same API client given in the access token. + + operationId: getBookingById + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain booking + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE" + BOOKING_UNAVAILABLE: + $ref: "#/components/examples/BOOKING_UNAVAILABLE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:read" + + delete: + tags: + - Device QoS Booking + summary: Deletes a QoS Booking + description: | + Release resources related to a QoS Booking. + + If the notification callback is provided and the booking status was `SCHEDULED` or `AVAILABLE`, when the deletion is completed, the client will receive, in addition to the response, a `BOOKING_STATUS_CHANGED` event with + - `status` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `status` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. + - The QoS Booking must have been created by the same API client given in the access token. + operationId: deleteBooking + parameters: + - $ref: "#/components/parameters/BookingId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Booking deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `SCHEDULED` or `AVAILABLE` with `statusInfo` set to `DELETE_REQUESTED`. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/BookingInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:delete" + + /retrieve-device-qos-bookings: + post: + tags: + - Device QoS Booking + summary: Gets the QoS Booking for a device + description: | + Querying for QoS Booking resource information details for a device. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS Booking must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The QoS Booking must have been created by the same API client given in the access token. + - If no QoS booking is found for the requested device, an empty array is returned. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + + operationId: retrieveBookingByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve a booking by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingByDevice" + required: true + responses: + "200": + description: Returns the QoS booking information for a given device. A device may have multiple bookings (for several times and locations), thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveBookingsOutput" + examples: + RETRIEVE_BOOKINGS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_ONE_ITEM" + RETRIEVE_BOOKINGS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_BOOKINGS_NO_ITEMS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-booking:device-qos-bookings:retrieve-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + BookingId: + name: bookingId + in: path + description: Booking ID that was obtained from the createBooking operation + required: true + schema: + $ref: "#/components/schemas/BookingId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + BookingId: + description: Booking Identifier in UUID format + type: string + format: uuid + + BaseBookingInfo: + description: Common attributes of a QoS Booking + type: object + properties: + qosProfile: + $ref: "#/components/schemas/QosProfileName" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + devicePorts: + description: The ports used locally by the device for flows to which the requested QoS profile should apply. If omitted, then the qosProfile will apply to all flows between the device and the specified application server address and ports + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationServerPorts: + description: A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered, using the HTTP protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + + BookingInfo: + description: | + Booking related information returned in responses. + Optional device object only to be returned if provided in createBooking. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in createBooking). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time of QoS Booking creation. + allOf: + - $ref: "#/components/schemas/BaseBookingInfo" + - type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + startTime: + description: Date and time when QoS profile is scheduled to become available. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + duration: + description: | + Session duration in seconds. Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + - When `qosStatus` is "REQUESTED" or "SCHEDULED", the value is the duration to be scheduled, granted by the implementation. + - When `qosStatus` is "AVAILABLE", the value is the overall duration since `startedAt`. + - When `qosStatus` is "UNAVAILABLE", the value is the overall effective duration since `startedAt` until the session was terminated. + type: integer + format: int32 + minimum: 1 + serviceArea: + $ref: "#/components/schemas/Area" + bookingId: + $ref: "#/components/schemas/BookingId" + startedAt: + description: Date and time when the Booking became "AVAILABLE". Not to be returned when `status` is "REQUESTED" or "SCHEDULED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - bookingId + - status + - startTime + - duration + - serviceArea + + CreateBooking: + description: Attributes to request a new QoS Booking + allOf: + - $ref: "#/components/schemas/BaseBookingInfo" + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + startTime: + description: Date and time when the API consumer requests the QoS profile to become available. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + duration: + description: + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). Implementations can grant the requested session duration or set a different duration from `startTime`, based on network policies or conditions. + type: integer + format: int32 + minimum: 1 + serviceArea: + $ref: "#/components/schemas/Area" + required: + - startTime + - duration + - serviceArea + + RetrieveBookingByDevice: + description: Attributes to look for QoS Booking + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveBookingsOutput: + description: QoS bookings for a given device + type: array + items: + $ref: "#/components/schemas/BookingInfo" + minItems: 0 + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an operator is offering can be retrieved by means of the [QoS Profile API](link TBC). + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-booking.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-booking.v0.status-changed: "#/components/schemas/EventStatusChanged" + + EventStatusChanged: + description: Event to notify a QoS Booking status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - bookingId + - status + properties: + bookingId: + $ref: "#/components/schemas/BookingId" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `status`. Currently `statusInfo` is only applicable when `status` is 'UNAVAILABLE'. + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the QoS Booking + * `DELETE_REQUESTED`- User requested the deletion of the QoS Booking + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Area: + description: Base schema for all areas + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + AREANAME: "#/components/schemas/AreaName" + + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + AREANAME - The area is defined as an area name. + enum: + - CIRCLE + - POLYGON + - AREANAME + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + description: Polygonal area. The Polygon should be a simple polygon, i.e. should not intersect itself. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + AreaName: + description: The value of "AreaName" might be predefined and only regional or even an operator-specific in this API version. As a prerequisite, the API Provider may offer API Consumer the "AreaName" values, which API consumer can request, in a preparation phase. And then API Consumers can select from the "AreaNames" as Service Areas. + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - areaName + properties: + areaName: + type: string + + PointList: + description: List of points defining a polygon + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: for the Commonalities release v0.4, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to clients. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + ApplicationServerIpv4Address: + type: string + example: "198.51.100.0/24" + description: | + IPv4 address may be specified in form
                                                              as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                                                              as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Status: + description: | + The current status of the requested QoS Booking. The status can be one of the following: + * `REQUESTED` - QoS booking has been requested but is still being processed. + * `SCHEDULED` - QoS booking has been granted for a future start time. + * `AVAILABLE` - The requested QoS profile has been activated for the device. + * `UNAVAILABLE` - The QoS booking request has been processed but is not scheduled or active. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - REQUESTED + - SCHEDULED + - AVAILABLE + - UNAVAILABLE + + StatusChanged: + description: | + The current status of a requested, scheduled or previously available QoS Booking. Applicable values in the event are: + * `SCHEDULED` - QoS booking has been granted for a future start time. + * `AVAILABLE` - The requested QoS profile has been activated for the device. + * `UNAVAILABLE` - The QoS booking request has been processed but is not scheduled or active. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - SCHEDULED + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateBooking400: + description: Bad Request when creating a QoS booking. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QOS_BOOKING.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QOS_BOOKING.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + BookingConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing booking for the same device. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + BookingUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QOS_BOOKING.NOT_MANAGED_AREA_TYPE + - QOS_BOOKING.AREA_NOT_COVERED + - QOS_BOOKING.INVALID_AREA + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QOS_BOOKING_422_NOT_MANAGED_AREA_TYPE: + summary: Not managed area type + description: The requested area type is currently not supported by implementation + value: + status: 422 + code: QOS_BOOKING.NOT_MANAGED_AREA_TYPE + message: "The requested area type is not managed" + QOS_BOOKING_422_AREA_NOT_COVERED: + summary: The area cannot be covered + description: The system is not able cover the requested area + value: + status: 422 + code: QOS_BOOKING.AREA_NOT_COVERED + message: "Unable to cover the requested area" + QOS_BOOKING_422_INVALID_AREA: + summary: Invalid area + description: The requested area value is not valid for the system. Details to be provided in the message. + value: + status: 422 + code: QOS_BOOKING.INVALID_AREA + message: "The requested area is too small" + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + BOOKING_AVAILABLE_WITH_DEVICE_RESPONSE: + summary: QoS booking status is available, with device included in response + description: QoS booking info when status is available, and request used a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + qosProfile: "QOS_L" + sink: "https://application-server.com/notifications" + device: + ipv4Address: + publicAddress: "203.0.113.0" + publicPort: 59765 + startTime: "2024-06-01T12:00:00Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "AVAILABLE" + + BOOKING_UNAVAILABLE: + summary: QoS booking is unavailable, with device not included in response + description: QoS booking info when status is unavailable due to network termination. Request used a 3-legged access token, or possibly a single device identifier + value: + qosProfile: "Acme2" + sink: "https://application-server.com/notifications" + startTime: "2024-06-01T12:00:00Z" + duration: 2428 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "UNAVAILABLE" + statusInfo: "NETWORK_TERMINATED" + + BOOKING_STATUS_CHANGED_EXAMPLE: + summary: Booking status changed + description: Cloud event example for status change to UNAVAILABLE due to DURATION_EXPIRED + value: + id: "83a0d986-0866-4f38-b8c0-fc65bfcda452" + source: "https://api.example.com/qod/v1/sessions/123e4567-e89b-12d3-a456-426614174000" + type: "org.camaraproject.qos-booking.v0.status-changed" + specversion: "1.0" + time: "2024-06-01T13:00:00Z" + data: + bookingId: "123e4567-e89b-12d3-a456-426614174000" + status: "UNAVAILABLE" + statusInfo: "DURATION_EXPIRED" + + RETRIEVE_BOOKINGS_ONE_ITEM: + summary: List of QoS sessions for the device + description: A single QoS session for the device is available + value: + - qosProfile: "QOS_L" + applicationServer: + ipv4Address: "0.0.0.0/0" + sink: "https://application-server.com/notifications" + device: + phoneNumber: "+123456789" + startTime: "2024-06-01T12:00:00Z" + duration: 3600 + serviceArea: + areaType: "CIRCLE" + center: + latitude: 50.735851 + longitude: 7.10066 + radius: 100 + bookingId: "3fa85f64-5717-4562-b3fc-2c963f66afa6" + startedAt: "2024-06-01T12:00:00Z" + status: "AVAILABLE" + + RETRIEVE_BOOKINGS_NO_ITEMS: + summary: No bookings found for the device + description: An empty array is returned when no bookings are found for the device + value: [] diff --git a/original/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist.md b/original/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..a43a786390df336fe0a418573fc550950ac11abc --- /dev/null +++ b/original/QoSBooking/documentation/API_documentation/qos-booking-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qos-booking v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                              public | stable
                                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/qos-booking.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/qos-booking.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/3YPVB) | diff --git a/original/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist.md b/original/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ecd071c47deef80b10d6f18d7520dffe4f385554 --- /dev/null +++ b/original/QoSBooking/documentation/API_documentation/qos-booking-and-assignment-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for qos-booking-and-assignment v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                              public | stable
                                                              public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/qos-booking-and-assignment.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | contained in API definition | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](code/Test_definitions/qos-booking-and-assignment.feature)| +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IYA5Cg) | diff --git a/original/QoSBooking/documentation/SupportingDocuments/README.MD b/original/QoSBooking/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/QoSBooking/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/QualityOnDemand/README.md b/original/QualityOnDemand/README.md new file mode 100644 index 0000000000000000000000000000000000000000..4b35980bec0821bf3c796b3c194893163c295d01 --- /dev/null +++ b/original/QualityOnDemand/README.md @@ -0,0 +1,65 @@ + + + + + + + + + +# QualityOnDemand + +Incubating API Repository to evolve and maintain the definitions and documentation of QualityOnDemand Service API(s) within the Sub Project [Connectivity Quality Management](https://lf-camaraproject.atlassian.net/wiki/x/hAClB) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) + +## Scope + +* Service APIs for “Quality on Demand” (see APIBacklog.md) +* The Service APIs provide the API consumer with the ability to: + * retrieve the possible quality options (profiles) from the network (qos-profiles) + * set the quality for a connection of a mobile device or a home device within the access network + * dynamically, for a selected session of a specific duration (quality-on-demand) + * provisioned, applying the same quality each time the device connects to the network (qod-provisioning) + * get a notification if the network cannot fulfill the requested quality profile (quality-on-demand, qod-provisioning) +* Describe, develop, document and test the APIs (with 1–2 Service Providers) +* Started: October 2021 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.2](https://github.com/camaraproject/QualityOnDemand/releases/tag/r3.2) (Fall25), with the following API versions: + * **qos-profiles v1.1.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/qos-profiles.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-profiles.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-profiles.yaml) + * **qos-provisioning v0.3.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/qos-provisioning.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-provisioning.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/qos-provisioning.yaml) + * **quality-on-demand v1.1.0** + [[YAML]](https://github.com/camaraproject/QualityOnDemand/blob/r3.2/code/API_definitions/quality-on-demand.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/quality-on-demand.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/r3.2/code/API_definitions/quality-on-demand.yaml) +* The latest public release is always available here: https://github.com/camaraproject/QualityOnDemand/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/QualityOnDemand/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/QualityOnDemand/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: bi-weekly, Friday, 13:00 UTC (14:00 CET, 15:00 CEST). For date/time of the next meeting, see previous meeting minutes + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94112812156?password=f238d6af-c959-48d7-a862-abdb3c648e40) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/XCPe) +* Mailing List + * Subscribe / unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/QualityOnDemand/code/API_definitions/qos-profiles.yaml b/original/QualityOnDemand/code/API_definitions/qos-profiles.yaml new file mode 100644 index 0000000000000000000000000000000000000000..72f8363f2745d213d1dd748cc31d7361826fb6ab --- /dev/null +++ b/original/QualityOnDemand/code/API_definitions/qos-profiles.yaml @@ -0,0 +1,852 @@ +openapi: 3.0.3 +info: + title: QoS Profiles + description: | + The Quality-of-Service (QoS) Profiles API provides a set of predefined network performance characteristics, such as latency, throughput, and priority, identified by a unique name. These profiles allow application developers to specify the desired network behavior for their application's data traffic, ensuring optimal performance. By selecting an appropriate QoS profile, developers can request stable latency (reduced jitter) or throughput for specific data flows between client devices and application servers when used by the Quality-On-Demand APIs. + + # Introduction + + QoS Profiles are used in conjunction with other Quality-On-Demand APIs, to offer the API consumer the capability to request for stable latency (reduced jitter) or throughput for some specified application data flows between application clients (within a user device) and Application Servers (backend services). The API consumer has a pre-defined set of Quality of Service (QoS) profiles which they could choose from depending on their latency or throughput requirements. The QoS profiles are defined by the API provider and are mapped to the connectivity characteristics of the supported networks. + + # API functionality + + The QoS Profiles API provides the following functionality: + - Discover all QoS profiles offered by the API provider + - Discover the available QoS profiles for a specific device + - Retrieve the characteristics of a specific QoS profile by name + + How QoS profiles are mapped to connectivity characteristics are subject to agreements between the API provider and the API consumer. Within the CAMARA project, you can find a sample for such a mapping of QoS profiles. [CAMARA QoS Profiles Mapping Table (REFERENCE DRAFT)](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/API_documentation/QoSProfile_Mapping_Table.md) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + The two operations defined by this API (`getQosProfile` and `retrieveQoSProfiles`) both allow the API consumer to use a three-legged access token to specify a target device as a query filter. When provided, only profiles available to the specified target device will be returned. Additionally, when a two-legged access token is used, the operation `retrieveQoSProfiles` allows the API consumer to optionally specify the target device in the request body. + + Hence, for the `retrieveQoSProfiles` operation: + - When invoked using a two-legged access token, the optional input device object will be used as filter if present. + + - When invoked using a three-legged access token, this optional identifier in the request body MUST NOT be provided, as the device to filter will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the device can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify a single device from that phone number. When filtering QoS profiles by device in such scenarios, one of the following options should be used: + - Use the authorisation code flow to obtain a 3-legged access token, which will automatically identify the intended device + - Identify the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/qos-profiles/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: QoS Profiles + description: Manage QoS Profiles + +paths: + /retrieve-qos-profiles: + post: + tags: + - QoS Profiles + summary: Retrieve QoS profiles + description: | + Returns all QoS Profiles that match the given criteria. + **NOTES:** + - The access token may be either a 2-legged or 3-legged access token. + - If the access token is 3-legged, all returned QoS Profiles will be available to the subject (device) associated with the access token. + - If the access token is 2-legged and a device filter is provided, all returned QoS Profiles will be available to that device. If multiple device identifiers are provided within the device property, only QoS Profiles available to the device identifier chosen by the implementation will be returned, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. Additionally, this call may include complex data structures. + [CAMARA API Design Guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/API-design-guidelines.md#post-or-get-for-transferring-sensitive-or-complex-data) + + security: + - openId: + - qos-profiles:read + operationId: retrieveQoSProfiles + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to query QoS Profiles for a given device + content: + application/json: + schema: + $ref: "#/components/schemas/QosProfileDeviceRequest" + required: true + responses: + "200": + description: Contains information about QoS Profiles + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/QosProfile" + examples: + List of QoS Profiles: + $ref: "#/components/examples/LIST_OF_QOS_PROFILES" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /qos-profiles/{name}: + get: + tags: + - QoS Profiles + summary: "Get QoS Profile for a given name" + operationId: getQosProfile + description: | + Returns a QoS Profile that matches the given name. + + The access token may be either a 2-legged or 3-legged access token. If the access token is 3-legged, a QoS Profile is only returned if available to all subjects associated with the access token. + + security: + - openId: + - qos-profiles:read + parameters: + - name: name + in: path + description: Qos Profile name + required: true + schema: + $ref: "#/components/schemas/QosProfileName" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about QoS Profiles + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/QosProfile" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + QosProfile: + description: | + Data type with attributes of a QosProfile + type: object + properties: + name: + $ref: "#/components/schemas/QosProfileName" + description: + description: | + A description of the QoS profile. + type: string + example: "QoS profile for video streaming" + status: + $ref: "#/components/schemas/QosProfileStatusEnum" + countryAvailability: + description: | + A list of countries, and optionally networks, for which the API provider makes the profile available. + - When profiles are filtered for a specific device (i.e. using a 3-legged access token or an explicit device filter parameter), the profile can be used by that device in any of these countries when connected to any of the listed networks (assuming roaming is permitted for networks that are not the device's home network), or the API provider's own network if no networks are listed + - When there is no device filter, availability for a given country means that the QoS profile may be available to some devices connected to the listed networks in that country (or to the API provider’s default network if none are listed). However, this does not imply that the profile is available to all devices, or that a particular device will be able to use the profile across all listed countries or networks. In particular, the response does not provide enough information to determine availability for roaming for specific devices; consumers should query the API with a specific device identifier to get definitive availability. + - If this field is not present in the QoS profile, no assumption can be made about the availability of the profile in any given country or for any given network + allOf: + - $ref: "#/components/schemas/Availability" + targetMinUpstreamRate: + description: | + This is the target minimum upload speed for the QoS profile. + It represents the minimum rate that the network attempts to deliver. + Please note that this is a target value—the network might not always be able to provide this rate under all conditions. + It helps ensure that applications like video calls or live streaming perform consistently. + allOf: + - $ref: "#/components/schemas/Rate" + maxUpstreamRate: + description: | + The maximum best effort data + allOf: + - $ref: "#/components/schemas/Rate" + maxUpstreamBurstRate: + description: | + When defined, this is the maximum upstream burst rate for the QoS profile, that will enable + the network to burst data at a higher rate than the maxUpstreamRate for a period of time. + allOf: + - $ref: "#/components/schemas/Rate" + targetMinDownstreamRate: + description: | + This is the target minimum download speed for the QoS profile. + It represents the minimum rate that the network attempts to deliver. + Please note that this is a target value—the network might not always be able to provide this rate under all conditions. + It helps ensure that applications like video calls or live streaming perform consistently. + allOf: + - $ref: "#/components/schemas/Rate" + maxDownstreamRate: + description: | + The maximum best effort rate + allOf: + - $ref: "#/components/schemas/Rate" + maxDownstreamBurstRate: + description: | + When defined, this is the maximum downstream burst rate for the QoS profile, that will enable + the network to burst data at a higher rate than the maxDownstreamRate for a period of time. + This can result in improved user experience when there is additional network capacity. + For instance, when a user is streaming a video, the network can burst data at a higher rate + to fill the buffer, and then return to the maxUpstreamRate once the buffer is full. + allOf: + - $ref: "#/components/schemas/Rate" + minDuration: + description: | + The shortest time period that this profile can be deployed. + allOf: + - $ref: "#/components/schemas/Duration" + maxDuration: + description: | + The maximum time period that this profile can be deployed. + Overall session duration must not exceed this value. This includes the initial requested duration plus any extensions. + allOf: + - $ref: "#/components/schemas/Duration" + priority: + type: integer + example: 20 + description: | + Priority levels allow efficient resource allocation and ensure optimal performance + for various services in each technology, with the highest priority traffic receiving + preferential treatment. + The lower value the higher priority. + Not all access networks use the same priority range, so this priority will be + scaled to the access network's priority range. + format: int32 + minimum: 1 + maximum: 100 + packetDelayBudget: + description: | + The packet delay budget is the maximum allowable one-way latency between the customer's device + and the gateway from the operator's network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, such as voice calls, + video streaming, and data. + The end-to-end or round trip latency will be about two times this value plus the latency not controlled + by the operator + allOf: + - $ref: "#/components/schemas/Duration" + jitter: + description: | + The jitter requirement aims to limit the maximum variation in round-trip + packet delay for the 99th percentile of traffic, following ITU Y.1540 + standards. It considers only acknowledged packets in a session, which are + packets that receive a confirmation of receipt from the recipient (e.g., + using TCP). This requirement helps maintain consistent latency, essential + for real-time applications such as VoIP, video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + packetErrorLossRate: + type: integer + description: | + This field specifies the acceptable level of data loss during transmission. + The value is an exponent of 10, so a value of 3 means that up to 10⁻³, or 0.1%, of the + data packets may be lost. This setting is part of a broader system that categorizes + different types of network traffic (like phone calls, video streams, or data transfers) + to ensure they perform reliably on the network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + l4sQueueType: + type: string + enum: + - non-l4s-queue + - l4s-queue + - mixed-queue + description: | + + **NOTE**: l4sQueueType is experimental and could change or be removed in a future release. + + Specifies the type of queue for L4S (Low Latency, Low Loss, Scalable Throughput) traffic management. L4S is an advanced queue management approach designed to provide ultra-low latency and high throughput for internet traffic, particularly beneficial for interactive applications such as gaming, video conferencing, and virtual reality. + + **Queue Type Descriptions:** + + - **non-l4s-queue**: + A traditional queue used for legacy internet traffic that does not utilize L4S enhancements. It provides standard latency and throughput levels. + + - **l4s-queue**: + A dedicated queue optimized for L4S traffic, delivering ultra-low latency, low loss, and scalable throughput to support latency-sensitive applications. + + - **mixed-queue**: + A shared queue that can handle both L4S and traditional traffic, offering a balance between ultra-low latency for L4S flows and compatibility with non-L4S flows. + + externalDocs: + description: For more details, refer to the L4S standard. + url: https://datatracker.ietf.org/doc/rfc9330/ + serviceClass: + type: string + description: | + + **NOTE**: serviceClass is experimental and could change or be removed in a future release. + + The name of a Service Class, representing a QoS Profile designed to provide optimized behavior for a specific application type. While DSCP values are commonly associated with Service Classes, their use may vary across network segments and may not be applied throughout the entire end-to-end QoS session. This aligns with the serviceClass concept used in HomeDevicesQoQ for consistent terminology. + + Service classes define specific QoS behaviors that map to DSCP (Differentiated Services Code Point) values or Microsoft QoS traffic types. + + The supported mappings are: + 1. Values aligned with the [RFC4594](https://datatracker.ietf.org/doc/html/rfc4594) guidelines for differentiated traffic classes. + 2. Microsoft [QOS_TRAFFIC_TYPE](https://learn.microsoft.com/en-us/windows/win32/api/qos2/ne-qos2-qos_traffic_type) values for Windows developers. + + **Supported Service Classes**: + + | Service Class Name | DSCP Name | DSCP value (decimal) | DCSP value (binary) | Microsoft Value | Application Examples | + |-----------------------|-----------|----------------------|---------------------|-----------------|----------------------------------------------------------------------| + | Microsoft Voice | CS7 | 56 | 111000 | 4,5 | Microsoft QOSTrafficTypeVoice and QOSTrafficTypeControl | + | Microsoft Audio/Video | CS5 | 40 | 101000 | 2,3 | Microsoft QOSTrafficTypeExcellentEffort and QOSTrafficTypeAudioVideo | + | Real-Time Interactive | CS4 | 32 | 100000 | | Video conferencing and Interactive gaming | + | Multimedia Streaming | AF31 | 26 | 011010 | | Streaming video and audio on demand | + | Broadcast Video | CS3 | 24 | 011000 | | Broadcast TV & live events | + | Low-Latency Data | AF21 | 18 | 010010 | | Client/server transactions Web-based ordering | + | High-Throughput Data | AF11 | 10 | 001010 | | Store and forward applications | + | Low-Priority Data | CS1 | 8 | 001000 | 1 | Any flow that has no BW assurance - also: | + | | | | | | Microsoft QOSTrafficTypeBackground | + | Standard | DF(CS0) | 0 | 000000 | 0 | Undifferentiated applications - also: | + | | | | | | Microsoft QOSTrafficTypeBestEffort | + enum: + - microsoft_voice # Microsoft QOSTrafficTypeVoice or Control + - microsoft_audio_video # Microsoft QOSTrafficTypeExcellentEffort or AudioVideo + - real_time_interactive # Video conferencing and interactive gaming + - multimedia_streaming # Streaming video or audio on demand + - broadcast_video # Broadcast TV and live events + - low_latency_data # Client/server transactions Web-based ordering + - high_throughput_data # STore and forward applications + - low_priority_data # Low-priority background traffic + - standard # Default traffic class + example: real_time_interactive + required: + - name + - status + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profile names like `QOS_E`, `QOS_S`, `QOS_M`, and `QOS_L` + - A searchable descriptive name + type: string + example: voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + Duration: + description: Specification of duration + type: object + properties: + value: + description: Quantity of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + QosProfileStatusEnum: + description: | + The current status of the QoS Profile + - `ACTIVE`- QoS Profile is available to be used + - `INACTIVE`- QoS Profile is not currently available to be deployed + - `DEPRECATED`- QoS profile is actively being used in a QoD session, but can not be deployed in new QoD sessions + type: string + enum: + - ACTIVE + - INACTIVE + - DEPRECATED + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + QosProfileDeviceRequest: + description: | + Request object for QoS Profiles for a given device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + name: + $ref: "#/components/schemas/QosProfileName" + status: + $ref: '#/components/schemas/QosProfileStatusEnum' + + Availability: + description: A list of countries, and optionally networks, for which the API provider makes the profile available + type: array + items: + type: object + required: + - countryName + properties: + countryName: + description: The two letter ISO 3166-2 country code for the country in which the QoS profile is available in at least one network + type: string + pattern: ^[A-Z]{2}$ + example: "GB" + networks: + description: A list of networks within the country for which the QoS profile is available from the API provider + type: array + items: + description: The network identifier. For mobile networks, this is the PLMN Identifier (MCC + MNC), which is a 5 or 6 digit integer. + type: string + example: "23591" + example: ["23591", "23415"] + example: {"countryName": "GB", "networks": ["23591", "23415"]} + example: [{"countryName": "GB", "networks": ["23591", "23415"]}, {"countryName": "DE", "networks": ["26202"]}] + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and the specified application server, unless further restricted by the optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + LIST_OF_QOS_PROFILES: + summary: A list of QoS profiles with a single entry + description: Example response when requesting a list of QoS profiles + value: + - name: "voice" + description: "QoS profile for high-quality interactive voice" + status: "ACTIVE" + targetMinUpstreamRate: + value: 100 + unit: "kbps" + targetMinDownstreamRate: + value: 100 + unit: "kbps" + minDuration: + value: 1 + unit: "Days" + maxDuration: + value: 10 + unit: "Days" + priority: 10 + packetDelayBudget: + value: 50 + unit: "Milliseconds" + jitter: + value: 5 + unit: "Milliseconds" + packetErrorLossRate: 3 + l4sQueueType: "non-l4s-queue" diff --git a/original/QualityOnDemand/code/API_definitions/qos-provisioning.yaml b/original/QualityOnDemand/code/API_definitions/qos-provisioning.yaml new file mode 100644 index 0000000000000000000000000000000000000000..d5439873e7b8572fc39ce46b05cac9a41ecff725 --- /dev/null +++ b/original/QualityOnDemand/code/API_definitions/qos-provisioning.yaml @@ -0,0 +1,1258 @@ +openapi: 3.0.3 +info: + title: QoS Provisioning + description: | + The Quality of Service (QoS) Provisioning API provides a programmable interface for developers to request the indefinite assignment of a specified QoS profile to all traffic being sent or received by a specified device. + + The association resulting from the QoS provisioning request is represented by a QoS assignment record (or QoS assignment for short) that includes information about the date of assignment, the QoS profile assigned to a device, the assignment status, etc., as well as an `assignmentId` that uniquely identifies this record for later use. + + Additionally, this API configures the network to apply the requested QoS profile to a specified device whenever the device is connected to the network, until the assignment is revoked. + + # Relevant terms and definitions + + * **QoS profiles and QoS profile labels**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that a network operator is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API service provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone Number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the provisioning details. If only a single device identifier is provided, the implementation may or may not include the device identifier in the assignment details. + + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Notification URL and token**: + API consumers may provide a callback URL (`sink`) on which notifications about all status change events (eg. assignment termination) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. + + # Resources and Operations overview + The API defines four operations: + + - An operation to assign a QoS profile for a given device indefinitely. + - An operation to get the information about a specific QoS assignment record, identified by its `assignmentId`. + - An operation to get the details of a QoS assignment record for a given device. + - An operation to revoke the assignment of a QoS profile to a given device, identified by the `assignmentId`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + - If the requested `qosProfile` exists but is currently not available or incompatible for the QoS assignment (e.g., its status is INACTIVE or DEPRECATED, or its characteristics are not compatible with QoS Provisioning service), then the server will return an error with the `422 QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE` error code. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the QoS profile should apply from that phone number. If the phone number is used as the device identifier when assigning a QoS profile in a multi-SIM scenario, the API may respond with an error, apply the QoS profile to all devices in the multi-SIM group, or apply the QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/qos-provisioning/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +tags: + - name: QoS Assignment + description: Manage the permanent assignment of a QoS profile to a device + +paths: + /qos-assignments: + post: + tags: + - QoS Assignment + summary: Triggers the provisioning process for the assignment of a QoS profile to a device + description: | + Initiates the assignment of a specific QoS profile to a given device when connected to the operator's network. + + - If the QoS profile assignment is completed synchronously, the response will be 201 with `status` = `AVAILABLE`. + - If the QoS profile assignment request is accepted but not yet completed, the response will be 201 with `status` = `REQUESTED`. + - If the operator determines synchronously that the QoS profile assignment request cannot be fulfilled, the response will be 201 with `status` = `UNAVAILABLE`. + + - If the request includes the `sink` and `sinkCredential` properties, the client will receive a `status-changed` event with the outcome of the process. The event will be sent also for synchronous operations. + + **NOTES:** + - When the assignment status becomes `UNAVAILABLE`, the QoS profile assignment is not immediately released, but will get deleted automatically, at earliest 360 seconds after. + + This behavior allows API consumers that are not receiving notification events but are polling, to get the QoS profile assignment status information. Before a client can attempt to create a new QoS profile assignment for the same device, they must release the previous assignment resources with an explicit `delete` operation if not yet automatically deleted. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createQosAssignment + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to assign a QoS profile to a device + content: + application/json: + schema: + $ref: "#/components/schemas/CreateAssignment" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: Assignment notifications callback + description: | + Important: this endpoint is to be implemented by the API consumer. + The QoS server will call this endpoint whenever any QoS assignment change related event occurs. + Currently only `ASSIGNMENT_STATUS_CHANGED` event is defined. + operationId: postQosAssignmentNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + ASSIGNMENT_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/ASSIGNMENT_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Assignment created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + Successful QoS Profile Assignment Creation: + $ref: "#/components/examples/ASSIGNMENT_CREATION_EXAMPLE" + Successful QoS Profile Assignment Creation with Device in the response: + $ref: "#/components/examples/ASSIGNMENT_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/CreateAssignment400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/AssignmentConflict409" + "422": + $ref: "#/components/responses/CreateAssignment422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:create" + + /qos-assignments/{assignmentId}: + get: + tags: + - QoS Assignment + summary: Get the QoS profile assignment information identified by an assignment record ID + description: | + Querying for details about the QoS profile assignment + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS profile assignment must also be associated with the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + operationId: getQosAssignmentById + parameters: + - $ref: "#/components/parameters/assignmentId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Returns information about certain assignment + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + ASSIGNMENT_AVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE" + ASSIGNMENT_UNAVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_UNAVAILABLE" + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:read" + + delete: + tags: + - QoS Assignment + summary: Revokes a QoS profile assignment identified by an assignment record ID + description: | + Revokes the assignment of a QoS profile to a device performed by a previous assignment operation. + + If the notification callback is provided and the assignment status was `AVAILABLE`, when the process is completed, the API consumer will receive in addition to the response a `ASSIGNMENT_STATUS_CHANGED` event with + - `status` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `status` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the QoS profile assignment must also be associated with the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + operationId: revokeQosAssignment + parameters: + - $ref: "#/components/parameters/assignmentId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Assignment revoked + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Deletion request accepted to be processed. It applies for an async deletion process. `status` in the response will be `AVAILABLE` with `statusInfo` set to `DELETE_REQUESTED`. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:delete" + + /retrieve-qos-assignment: + post: + tags: + - QoS Assignment + summary: Returns the assignment record details of the QoS profile assignment for a device + description: | + Returns the details of the record for the assignment of a QoS profile to a device, if any. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + - The QoS profile assignment must have been created by the same API consumer given in the access token. + - If no QoS profile assignment is found for the device, an error response 404 is returned with code "NOT_FOUND". + - This call uses the POST method instead of GET to comply with the [CAMARA Commonalities guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/CAMARA-API-Design-Guide.md#65-post-or-get-for-transferring-sensitive-or-complex-data) for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + + operationId: getQosAssignmentByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to retrieve an assignment record by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveAssignmentByDevice" + required: true + responses: + "200": + description: Returns information about the QoS profile assignment for the device. + + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/AssignmentInfo" + examples: + ASSIGNMENT_AVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE" + ASSIGNMENT_UNAVAILABLE: + $ref: "#/components/examples/ASSIGNMENT_UNAVAILABLE" + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + $ref: "#/components/examples/ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "qos-provisioning:qos-assignments:read-by-device" + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + + parameters: + assignmentId: + name: assignmentId + in: path + description: Identifier of the assignment record for the QoS profile assignment, that was created by the `createQosAssignment` operation + required: true + schema: + $ref: "#/components/schemas/AssignmentId" + + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + AssignmentId: + description: Identifier of the assignment record for the QoS profile assignment, that was created by the `createQosAssignment` operation + type: string + format: uuid + + BaseAssignmentInfo: + description: Common attributes of the assignment record for a QoS profile assignment + type: object + properties: + device: + $ref: "#/components/schemas/Device" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + required: + - qosProfile + + AssignmentInfo: + description: | + Information about a QoS profile assignment returned in responses. + Optional device object only to be returned if provided in `createQosAssignment`. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in assignQosProfile). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time the QoS profile assignment was created. + + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/DeviceResponse" + - $ref: "#/components/schemas/BaseAssignmentInfo" + - type: object + properties: + assignmentId: + $ref: "#/components/schemas/AssignmentId" + startedAt: + description: Date and time when the QoS profile assignment became "AVAILABLE". Not to be returned when `status` is "REQUESTED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:00Z" + status: + $ref: "#/components/schemas/Status" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - assignmentId + - status + + CreateAssignment: + description: Attributes to request a new QoS profile assignment + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + - $ref: "#/components/schemas/BaseAssignmentInfo" + + RetrieveAssignmentByDevice: + description: Attributes to look for a QoS profile assignment + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now. + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur + after the termination of the requested assignment, allowing the client to be notified of any changes during the + assignment's existence. If the token expires while the assignment is still active, the client will stop receiving notifications. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the service providers implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an API provider is offering may be retrieved by means of the QoS Profile API (qos-profile) or agreed on onboarding time. + type: string + example: QCI_1_voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific Provider Implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.qos-provisioning.v0.status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + type: string + enum: + - "1.0" + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - "application/json" + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: "type" + mapping: + org.camaraproject.qos-provisioning.v0.status-changed: "#/components/schemas/EventStatusChanged" + + EventStatusChanged: + description: Event to notify a QoS provisioning status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - assignmentId + - qosStatus + properties: + assignmentId: + $ref: "#/components/schemas/AssignmentId" + status: + $ref: "#/components/schemas/StatusChanged" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `status`: + * `NETWORK_TERMINATED` - Network terminated the QoS profile assignment + * `DELETE_REQUESTED` - User requested the deletion of the QoS profile assignment + + type: string + enum: + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Device: + description: | + End-user equipment able to connect to the network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + Status: + description: | + The current status of the requested QoS profile assignment. The status can be one of the following: + * `REQUESTED` - QoS profile assignment has been requested but is still being processed. + * `AVAILABLE` - The requested QoS profile has been assigned to the device, and is active. + * `UNAVAILABLE` - The QoS profile assignment request has been processed but is not active. `statusInfo` may provide additional information about the reason for the unavailability. + enum: + - REQUESTED + - AVAILABLE + - UNAVAILABLE + + StatusChanged: + description: | + The current status of a requested or previously available QoS profile assignment. Applicable values in the event are: + * `AVAILABLE` - The requested QoS profile has been assigned to the device, and is active. + * `UNAVAILABLE` - A requested or previously available QoS profile assignment is now unavailable. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + CreateAssignment400: + description: Bad Request with additional errors for implicit notifications + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + AssignmentConflict409: + description: Assignment conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + ASSIGNMENT_409_CONFLICT: + description: The requested provisioning process conflicts with an existing one + value: + status: 409 + code: CONFLICT + message: There is another existing provisioning for the same device + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token.ç + + CreateAssignment422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QOS_PROVISIONING_422_QOS_PROFILE_NOT_APPLICABLE: + description: The requested QoS Profile exists but cannot be used for the QoS assignment. + value: + status: 422 + code: QOS_PROVISIONING.QOS_PROFILE_NOT_APPLICABLE + message: The requested QoS Profile is not compatible with the QoS Provisioning service. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + ASSIGNMENT_CREATION_EXAMPLE: + summary: Successful assignment creation without device in the assignment details + description: Example response after a new QoS profile assignment has been created using a 3-legged access token, or possibly a single device identifier + value: + qosProfile: QOS_L + sink: https://application-server.com/callback + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + status: REQUESTED + + ASSIGNMENT_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful assignment creation with device in the assignment details + description: Example response after a new QoS profile assignment has been created using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + device: + phoneNumber: "+123456789" + qosProfile: QOS_L + sink: https://application-server.com/callback + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + status: REQUESTED + + ASSIGNMENT_AVAILABLE: + summary: QoS assignment status is available with device in the assignment details + description: The QoS profile assignment has become available, and the device to which the assignment applies is included in the assignment details + value: + device: + phoneNumber: "+123456789" + qosProfile: QOS_L + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: AVAILABLE + + ASSIGNMENT_UNAVAILABLE: + summary: QoD provisioning status is unavailable + description: The asssignment could not be created or is not active anymore + value: + qosProfile: QOS_L + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: UNAVAILABLE + statusInfo: NETWORK_TERMINATED + + ASSIGNMENT_AVAILABLE_WITHOUT_DEVICE: + summary: QoS assignment status is available + description: Device is optional in responses and must not be provided if it was not provided in the request + value: + qosProfile: QOS_M + sink: https://application-server.com/callback + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "eyJhbGciOiJIUzI1NiIsInR..." + accessTokenExpiresUtc: "2024-12-01T12:00:00Z" + accessTokenType: bearer + assignmentId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-05-12T17:32:01Z" + status: AVAILABLE + + ASSIGNMENT_STATUS_CHANGED_EXAMPLE: + description: Assignment status changed + summary: Cloud event example for QoD assignment status change to UNAVAILABLE due to NETWORK_TERMINATED + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: https://api.example.com/qos-provisioning/v0.4/qos-assignments/123e4567-e89b-12d3-a456-426614174000 + specversion: "1.0" + type: org.camaraproject.qos-provisioning.v0.status-changed + time: "2021-12-12T00:00:00Z" + data: + assignmentId: 123e4567-e89b-12d3-a456-426614174000 + status: UNAVAILABLE + statusInfo: NETWORK_TERMINATED diff --git a/original/QualityOnDemand/code/API_definitions/quality-on-demand.yaml b/original/QualityOnDemand/code/API_definitions/quality-on-demand.yaml new file mode 100644 index 0000000000000000000000000000000000000000..cd8431307a8f1fd1f7e35a82f6d3bfb71bbdd969 --- /dev/null +++ b/original/QualityOnDemand/code/API_definitions/quality-on-demand.yaml @@ -0,0 +1,1608 @@ +openapi: 3.0.3 +info: + title: Quality-On-Demand + description: | + The Quality-On-Demand (QoD) API provides a programmable interface for developers and other users (API consumers) to request stable latency or throughput managed by networks without the necessity to have an in-depth knowledge of the underlying network complexity (e.g. the 4G/5G system in case of a mobile network). + + # Introduction + + Industrial (IoT), VR/Gaming, live video streaming, autonomous driving and many other scenarios demand network communication quality and are sensitive to any change in transmission conditions. Being able to request a stable latency (reduced jitter) or prioritized throughput from the network can improve user experience substantially. + + The QoD API offers the application developers the capability to request for stable latency (reduced jitter) or throughput for some specified application data flows between application clients (within a user device) and application servers (backend services). The developer has a pre-defined set of Quality of Service (QoS) profiles which they could choose from depending on their latency or throughput requirements. + + ![QoD API Overview](https://raw.githubusercontent.com/camaraproject/QualityOnDemand/main/documentation/API_documentation/resources/QoD_latency_overview.PNG) + + The usage of the API is based on QoS session resources, which can be created (based on available QoS profiles), queried and deleted. The deletion of a requested session can be triggered by the API consumer or can be triggered automatically once the QoS session has reached its limit. + + # Relevant terms and definitions + + * **QOD service endpoint**: + The URL pointing to the RESTful resource of the QoD API. + + * **Authentication**: + Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the QoD API. + + * **QoS profiles**: + Latency, throughput or priority requirements of the application mapped to relevant QoS profile values. The set of QoS Profiles that an API provider is offering may be retrieved via the `qos-profiles` API (cf. https://github.com/camaraproject/QualityOnDemand/) or will be agreed during the onboarding with the API provider. + + * **Identifier for the device**: + At least one identifier for the device (user equipment) out of four options: IPv4 address, IPv6 address, Phone Number, or Network Access Identifier assigned by the mobile network operator for the device. Where more than one device identifier is provided, only one identifier will be selected by the implementation and this choice indicated to the API consumer in the session details. If only a single device identifier is provided, the implementation may or may not include the device identifier in the session details. + + Note: Network Access Identifier is defined for future use and will not be supported with this version of the API. + + * **Identifier for the application server**: + IPv4 and/or IPv6 address of the application server (application backend) + + * **App-Flow (between the application client and application server)**: + The precise application data flow the developer wants to prioritize and have stable latency or throughput for. This flow is in the current API version determined by the identified device and the application server. And it can be further elaborated with details such as ports or port-ranges. Future version of the API might allow more detailed flow identification features. + + * **Duration**: + Duration (in seconds) for which the QoS session (between application client and application server) should be created. Limits for session duration can be set by the implementation for the QoS profile. The user may request a termination before its expiration. + + * **Notification URL and token**: + The API consumer may provide a callback URL (`sink`) on which notifications about all status change events (eg. session termination) can be received from the API provider. This is an optional parameter. The notification will be sent as a CloudEvent compliant message. + If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version, `sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # API functionality + + The usage of the QoD API is based on QoS profile classes and parameters which define App-Flows. + Based on the API, QoS session resources can be created, queried, and deleted. Once an offered QoS profile class is requested, application users get a prioritized service with stable latency or throughput even in the case of congestion. The QoD API has the following characteristics: + + * A specified App-Flow is prioritized to ensure stable latency or throughput for that flow. + * The prioritized App-Flow is described by providing information such as device IP address (or other device identifier) & application server IP addresses and port/port-ranges. + * The developer specifies the duration for which they need the prioritized App-flow. + * Stable latency or throughput is requested by selecting from the list of QoS profiles made available by the service provider (e.g. QOS_E) to map latency and throughput requirements. + * The API consumer can optionally also specify callback URL (`sink` param) on which notifications for the session can be sent.
                                                              + + Following diagram shows the interaction between different components + + ![QoD Management API](https://raw.githubusercontent.com/camaraproject/QualityOnDemand/main/documentation/API_documentation/resources/QoD_details.PNG) + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` object is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + - If the requested `qosProfile` exists but is currently not available for creating a session (e.g., its status is INACTIVE or DEPRECATED), then the server will return an error with the `422 QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE` error code. + + # Multi-SIM scenario handling + + In multi-SIM scenarios where more than one mobile device is associated with a phone number (e.g. a smartphone with an associated smartwatch), it might not be possible to uniquely identify the device to which the enhanced QoS profile should apply from that phone number. If the phone number is used as the device identifier when creating a QoS session in a multi-SIM scenario, the API may respond with an error, apply the enhanced QoS profile to all devices in the multi-SIM group, or apply the enhanced QoS profile to a single device in the multi-SIM group which may not be the intended device. + + Possible solutions in such a scenario include: + - Using the authorisation code flow to obtain an access token, which will automatically identify the intended device + - Identifying the intended device from a unique identifier for that device, such as its source IP address and port + - Check with the SIM provider whether a unique "secondary" phone number is already associated with each device, and use the secondary phone number to identify the intended device if available + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/QualityOnDemand + +servers: + - url: "{apiRoot}/quality-on-demand/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: QoS Sessions + description: Manage QoS sessions + +paths: + /sessions: + post: + tags: + - QoS Sessions + summary: Creates a new session + description: | + Create QoS Session to manage latency/throughput priorities + + If the qosStatus in the API response is "AVAILABLE" and a notification callback is provided the API consumer will receive in addition to the response a + `QOS_STATUS_CHANGED` event notification with `qosStatus` as `AVAILABLE`. + + If the `qosStatus` in the API response is `REQUESTED`, the client will receive either + - a `QOS_STATUS_CHANGED` event notification with `qosStatus` as `AVAILABLE` after the network notifies that it has created the requested session, or + - a `QOS_STATUS_CHANGED` event notification with `qosStatus` as `UNAVAILABLE` and `statusInfo` as `NETWORK_TERMINATED` after the network notifies that it has failed to provide the requested session. + + A `QOS_STATUS_CHANGED` event notification with `qosStatus` as `UNAVAILABLE` will also be send if the network terminates the session before the requested duration expired + + **NOTES:** + - In case of a `QOS_STATUS_CHANGED` event with `qosStatus` as `UNAVAILABLE` and `statusInfo` as `NETWORK_TERMINATED` the resources of the QoS session are not directly released, but will get deleted automatically at earliest 360 seconds after the event. + + This behavior allows API consumers which are not receiving notification events but are polling to get the session information with the `qosStatus` `UNAVAILABLE` and `statusInfo` `NETWORK_TERMINATED`. Before a API consumer can attempt to create a new QoD session for the same device and flow period they must release the session resources with an explicit `delete` operation if not yet automatically deleted. + - The access token may be either 2-legged or 3-legged. See "Identifying the device from the access token" for further information + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + operationId: createSession + security: + - openId: + - quality-on-demand:sessions:create + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to create a new session + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSession" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + tags: + - Session notifications callback + summary: "Session notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The API provider will call this endpoint whenever any QoS session change (e.g. network termination) related event occurs. + Currently only QOS_STATUS_CHANGED event is defined. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + QOS_STATUS_CHANGED_EXAMPLE: + $ref: "#/components/examples/QOS_STATUS_CHANGED_EXAMPLE" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + security: + - {} + - notificationsBearerAuth: [] + responses: + "201": + description: Session created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + Successful Session Creation: + $ref: "#/components/examples/SESSION_CREATION_EXAMPLE" + Successful Session Creation With Device Disambiguation: + $ref: "#/components/examples/SESSION_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/CreateSessionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "409": + $ref: "#/components/responses/SessionInConflict409" + "422": + $ref: "#/components/responses/CreateSessionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}: + get: + tags: + - QoS Sessions + summary: Get QoS session information + description: | + Querying for QoS session resource information details + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the end user (and device) associated with the session must also be associated with the access token. + - The session must have been created by the same API client given in the access token + + operationId: getSession + security: + - openId: + - quality-on-demand:sessions:read + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Contains information about active session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + SESSION_AVAILABLE: + $ref: '#/components/examples/SESSION_AVAILABLE_EXAMPLE' + SESSION_UNAVAILABLE: + $ref: '#/components/examples/SESSION_UNAVAILABLE_EXAMPLE' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + delete: + tags: + - QoS Sessions + summary: Delete a QoS session + description: | + Release resources related to QoS session + + If the notification callback is provided and the `qosStatus` of the session was `AVAILABLE` the client will receive in addition to the response a `QOS_STATUS_CHANGED` event with + - `qosStatus` as `UNAVAILABLE` and + - `statusInfo` as `DELETE_REQUESTED` + There will be no notification event if the `qosStatus` was already `UNAVAILABLE`. + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. + - The session must must have been created by the same API consumer given in the access token + + operationId: deleteSession + security: + - openId: + - quality-on-demand:sessions:delete + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Session deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}/extend: + post: + tags: + - QoS Sessions + summary: "Extend the duration of an active session" + description: | + Extend the overall session duration of an active QoS session (with qosStatus = AVAILABLE). + The overall duration of the QoS session, including the additional extended duration, shall not exceed the maximum duration limit fixed for the QoS Profile. If the current duration plus the value of `requestedAdditionalDuration` exceeds the maximum limit, the new overall duration shall be capped to the maximum value allowed. + An example: For a QoS profile limited to a `maxDuration` of 50,000 seconds, a QoD session was originally created with duration 30,000 seconds. Before the session expires, the developer requests to extend the session by another 30,000 seconds: + - Previous duration: 30,000 seconds + - Requested additional duration: 30,000 seconds + - New overall session duration: 50,000 seconds (the maximum allowed) + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. + - The session must must have been created by the same API consumer given in the access token + + operationId: extendQosSessionDuration + security: + - openId: + - quality-on-demand:sessions:update + parameters: + - name: sessionId + in: path + description: Session ID that was obtained from the createSession operation + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to extend the duration of an active session + content: + application/json: + schema: + $ref: "#/components/schemas/ExtendSessionDuration" + required: true + responses: + "200": + description: Contains information about active session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SessionInfo" + examples: + SESSION_EXTENDED: + $ref: "#/components/examples/SESSION_EXTENDED_EXAMPLE" + SESSION_EXTENDED_WITH_DEVICE_RESPONSE: + $ref: "#/components/examples/SESSION_EXTENDED_EXAMPLE_WITH_DEVICE_RESPONSE" + "400": + $ref: "#/components/responses/GenericExtendSessionDuration400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "409": + $ref: "#/components/responses/SessionStatusConflict409" + "429": + $ref: "#/components/responses/Generic429" + + /retrieve-sessions: + post: + tags: + - QoS Sessions + summary: Get QoS session information for a device + description: | + Querying for QoS session resource information details for a device + + **NOTES:** + - The access token may be either 2-legged or 3-legged. + - If a 3-legged access token is used, the subject associated with the session must also be associated with the access token. In this case the optional `device` parameter MUST NOT be provided in the request. + - If a 2-legged access token is used, the device parameter must be provided and identify a device. + - The session must have been created by the same API consumer given in the access token + - If no QoS session is found for the requested device, an empty array is returned. + - This call uses the POST method instead of GET to comply with the CAMARA Commonalities guidelines for sending sensitive or complex data in API calls. Since the device field may contain personally identifiable information, it should not be sent via GET. + [CAMARA API Design Guidelines](https://github.com/camaraproject/Commonalities/blob/r3.3/documentation/CAMARA-API-Design-Guide.md#65-post-or-get-for-transferring-sensitive-or-complex-data) + + operationId: retrieveSessionsByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to get QoS session information by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsInput" + required: true + responses: + "200": + description: Returns the QoS sessions information for a given device. A device may have multiple sessions, thus the response is an array. An empty array is returned if no sessions are found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsOutput" + examples: + RETRIEVE_SESSIONS_ONE_ITEM: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EXAMPLE" + RETRIEVE_SESSIONS_ONE_ITEM_WITH_DEVICE_DISAMBIGUATION_REQUIRED: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EXAMPLE_WITH_DEVICE_RESPONSE" + RETRIEVE_SESSIONS_NO_ITEMS: + $ref: "#/components/examples/RETRIEVE_SESSIONS_EMPTY_EXAMPLE" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/GenericDevice404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + security: + - openId: + - "quality-on-demand:sessions:retrieve-by-device" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + description: Value for the x-correlator + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + SessionId: + description: Session ID in UUID format + type: string + format: uuid + + BaseSessionInfo: + description: Common attributes of a QoD session + type: object + properties: + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + devicePorts: + description: The ports used locally by the device for flows to which the requested QoS profile should apply. If omitted, then the qosProfile will apply to all flows between the device and the specified application server address and ports + allOf: + - $ref: "#/components/schemas/PortsSpec" + applicationServerPorts: + description: A list of single ports or port ranges on the application server + allOf: + - $ref: "#/components/schemas/PortsSpec" + qosProfile: + $ref: "#/components/schemas/QosProfileName" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events about all status changes of the session (e.g. session termination) shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: "#/components/schemas/SinkCredential" + required: + - applicationServer + - qosProfile + + SessionInfo: + description: | + Session related information returned in responses. + Note that the device object is defined as optional and will only to be returned if provided in createSession. If more than one type of device identifier was provided, only one identifier will be returned (at implementation choice and with the original value provided in createSession). + Please note that IP addresses of devices can change and get reused, so the original values may no longer identify the same device. They identified the device at the time of session creation. + allOf: + - type: object + properties: + device: + description: Disambiguates the device to which the session applies when multiple device identifiers were provided + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + - $ref: "#/components/schemas/BaseSessionInfo" + - type: object + properties: + sessionId: + $ref: "#/components/schemas/SessionId" + duration: + description: | + Session duration in seconds. Implementations can grant the requested session duration or set a different duration, based on network policies or conditions. + - When `qosStatus` is "REQUESTED", the value is the duration to be scheduled, granted by the implementation. + - When `qosStatus` is AVAILABLE", the value is the overall duration since `startedAt. When the session is extended, the value is the new overall duration of the session. + - When `qosStatus` is "UNAVAILABLE", the value is the overall effective duration since `startedAt` until the session was terminated. + type: integer + format: int32 + minimum: 1 + example: 3600 + startedAt: + description: Date and time when the QoS status became "AVAILABLE". Not to be returned when `qosStatus` is "REQUESTED". It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2024-06-01T12:00:00Z" + expiresAt: + description: | + Date and time of the QoS session expiration. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + - When `qosStatus` is "AVAILABLE", it is the limit time when the session is scheduled to finnish, if not terminated by other means. + - When `qosStatus` is "UNAVAILABLE", it is the time when the session was terminated. + - Not to be returned when `qosStatus` is "REQUESTED". + When the session is extended, the value is the new expiration time of the session. + type: string + format: date-time + example: "2024-06-01T13:00:00Z" + qosStatus: + $ref: "#/components/schemas/QosStatus" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - sessionId + - duration + - qosStatus + + CreateSession: + description: Attributes required to create a session + allOf: + - type: object + properties: + device: + $ref: "#/components/schemas/Device" + - $ref: "#/components/schemas/BaseSessionInfo" + - type: object + properties: + duration: + description: | + Requested session duration in seconds. Value may be explicitly limited for the QoS profile, as specified in the Qos Profile (see qos-profile API). Implementations can grant the requested session duration or set a different duration, based on network policies or conditions. + type: integer + format: int32 + minimum: 1 + example: 3600 + required: + - duration + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + PortsSpec: + description: Specification of several TCP or UDP ports + type: object + minProperties: 1 + properties: + ranges: + description: Range of TCP or UDP ports + type: array + minItems: 1 + items: + type: object + required: + - from + - to + properties: + from: + $ref: "#/components/schemas/Port" + to: + $ref: "#/components/schemas/Port" + ports: + description: Array of TCP or UDP ports + type: array + minItems: 1 + items: + $ref: "#/components/schemas/Port" + example: + ranges: + - from: 5010 + to: 5020 + ports: + - 5060 + - 5070 + + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. Token expiration should occur + after the termination of the requested session, allowing the client to be notified of any changes during the + sessions's existence. If the token expires while the session is still active, the client will stop receiving notifications. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. MUST not be used in this API version. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute UTC instant at which the token shall be considered expired. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + ExtendSessionDuration: + description: Attributes required to extend the duration of an active session + type: object + properties: + requestedAdditionalDuration: + description: | + Additional duration in seconds to be added to the current session duration. The overall session duration, including extensions, shall not exceed the maximum duration limit for the QoS Profile. + type: integer + format: int32 + minimum: 1 + example: 1800 + required: + - requestedAdditionalDuration + + QosProfileName: + description: | + A unique name for identifying a specific QoS profile. + This may follow different formats depending on the API provider implementation. + Some options addresses: + - A UUID style string + - Support for predefined profiles QOS_S, QOS_M, QOS_L, and QOS_E + - A searchable descriptive name + The set of QoS Profiles that an API provider is offering may be retrieved by means of the QoS Profile API (qos-profile) or agreed on onboarding time. + type: string + example: voice + minLength: 3 + maxLength: 256 + format: string + pattern: "^[a-zA-Z0-9_.-]+$" + + CloudEvent: + description: Event compliant with the CloudEvents specification + required: + - id + - source + - specversion + - type + - time + properties: + id: + description: Identifier of this event, that must be unique in the source context. + type: string + source: + description: Identifies the context in which an event happened in the specific provider implementation. + type: string + format: uri-reference + type: + description: The type of the event. + type: string + enum: + - "org.camaraproject.quality-on-demand.v1.qos-status-changed" + specversion: + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to Cloudevents 1.0.2 version) + type: string + enum: + - '1.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + data: + description: Event notification details payload, which depends on the event type + type: object + time: + description: | + Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.quality-on-demand.v1.qos-status-changed: "#/components/schemas/EventQosStatusChanged" + + EventQosStatusChanged: + description: Event to notify a QoS status change + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + type: object + description: Event details depending on the event type + required: + - sessionId + - qosStatus + properties: + sessionId: + $ref: "#/components/schemas/SessionId" + qosStatus: + $ref: "#/components/schemas/EventQosStatus" + statusInfo: + $ref: "#/components/schemas/StatusInfo" + required: + - data + + StatusInfo: + description: | + Reason for the new `qosStatus`. Currently `statusInfo` is only applicable when `qosStatus` is 'UNAVAILABLE'. + * `DURATION_EXPIRED` - Session terminated due to requested duration expired + * `NETWORK_TERMINATED` - Network terminated the session before the requested duration expired + * `DELETE_REQUESTED`- User requested the deletion of the session before the requested duration expired + + type: string + enum: + - DURATION_EXPIRED + - NETWORK_TERMINATED + - DELETE_REQUESTED + + Device: + description: | + End-user equipment able to connect to a network. Examples of devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + NOTE1: the network operator might support only a subset of these options. The API consumer can provide multiple identifiers to be compatible across different network operators. In this case the identifiers MUST belong to the same device. + NOTE2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + ApplicationServer: + description: | + A server hosting backend applications to deliver some business logic to clients. + + The developer can choose to provide the below specified device identifiers: + + * `ipv4Address` + * `ipv6Address` + type: object + properties: + ipv4Address: + $ref: "#/components/schemas/ApplicationServerIpv4Address" + ipv6Address: + $ref: "#/components/schemas/ApplicationServerIpv6Address" + minProperties: 1 + + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "203.0.113.0", + "publicPort": 59765 + } + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "203.0.113.0" + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and the specified application server, unless further restricted by the optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + ApplicationServerIpv4Address: + type: string + example: "198.51.100.0/24" + description: | + IPv4 address may be specified in form
                                                              as: + - address - an IPv4 number in dotted-quad form 1.2.3.4. Only this exact IP number will match the flow control rule. + - address/mask - an IP number as above with a mask width of the form 1.2.3.4/24. + In this case, all IP numbers from 1.2.3.0 to 1.2.3.255 will match. The bit width MUST be valid for the IP version. + + ApplicationServerIpv6Address: + type: string + example: "2001:db8:85a3:8d3:1319:8a2e:370:7344" + description: | + IPv6 address may be specified in form
                                                              as: + - address - The /128 subnet is optional for single addresses: + - 2001:db8:85a3:8d3:1319:8a2e:370:7344 + - 2001:db8:85a3:8d3:1319:8a2e:370:7344/128 + - address/mask - an IP v6 number with a mask: + - 2001:db8:85a3:8d3::0/64 + - 2001:db8:85a3:8d3::/64 + + QosStatus: + description: | + The current status of the requested QoS session. The status can be one of the following: + * `REQUESTED` - QoS has been requested by creating a session + * `AVAILABLE` - The requested QoS has been provided by the network + * `UNAVAILABLE` - The requested QoS cannot be provided by the network due to some reason + type: string + enum: + - REQUESTED + - AVAILABLE + - UNAVAILABLE + + EventQosStatus: + description: | + The current status of a requested or previously available session. Applicable values in the event are: + * `AVAILABLE` - The requested QoS has been provided by the network. + * `UNAVAILABLE` - A requested or previously available QoS session is now unavailable. `statusInfo` may provide additional information about the reason for the unavailability. + type: string + enum: + - AVAILABLE + - UNAVAILABLE + + ErrorInfo: + description: Common schema for errors + type: object + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + required: + - status + - code + - message + + RetrieveSessionsInput: + description: Parameters to get QoS session information by device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveSessionsOutput: + description: QoS session information for a given device + type: array + items: + $ref: "#/components/schemas/SessionInfo" + minItems: 0 + + responses: + CreateSessionBadRequest400: + description: Bad Request when creating a session + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: The requested duration is out of the allowed range for the specific QoS profile + value: + status: 400 + code: QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + + GenericExtendSessionDuration400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + DurationOutOfRangeForQoSProfile: + description: NOTE - this error response cannot be returned by the `/extend` operation and will be removed from the API definition in the next version. + value: + status: 400 + code: QUALITY_ON_DEMAND.DURATION_OUT_OF_RANGE + message: The requested duration is out of the allowed range for the specific QoS profile + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + + GenericDevice404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_DEVICE_NOT_FOUND: + description: Device identifier not found + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + + SessionInConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + example: + status: 409 + code: CONFLICT + message: Conflict with an existing session for the same device. + + SessionStatusConflict409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - QUALITY_ON_DEMAND.SESSION_EXTENSION_NOT_ALLOWED + examples: + SessionExtensionNotAllowed: + description: Session extension is in conflict with current session status + value: + status: 409 + code: QUALITY_ON_DEMAND.SESSION_EXTENSION_NOT_ALLOWED + message: Extending the session duration is not allowed in the current state ({qosStatus}). The session must be in the AVAILABLE state. + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + CreateSessionUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + QUALITY_ON_DEMAND_422_QOS_PROFILE_NOT_APPLICABLE: + description: The requested QoS Profile exists but cannot be used to create a session. + value: + status: 422 + code: QUALITY_ON_DEMAND.QOS_PROFILE_NOT_APPLICABLE + message: The requested QoS Profile is currently not available for session creation. + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + + examples: + SESSION_CREATION_EXAMPLE: + summary: Successful session creation with device not included in response + description: Example response after a new QoS session has been created using a 3-legged access token, or possibly a single device identifier + value: + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + qosStatus: REQUESTED + + SESSION_CREATION_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful session creation with device included in response + description: Example response after a new QoS session has been created using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier + value: + device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + qosStatus: REQUESTED + + SESSION_AVAILABLE_EXAMPLE: + summary: QoS session status is available + description: QoS session info when status is available + value: + duration: 3600 + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + SESSION_UNAVAILABLE_EXAMPLE: + summary: QoS session is unavailable + description: QoS session info when status is unavailable due to network termination + value: + duration: 2428 + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T12:40:28Z" + qosStatus: UNAVAILABLE + statusInfo: NETWORK_TERMINATED + + QOS_STATUS_CHANGED_EXAMPLE: + summary: QoS status changed + description: Cloud event example for QoS status change to UNAVAILABLE due to DURATION_EXPIRED + value: + id: 83a0d986-0866-4f38-b8c0-fc65bfcda452 + source: 'https://api.example.com/qod/v1/sessions/123e4567-e89b-12d3-a456-426614174000' + specversion: '1.0' + type: "org.camaraproject.quality-on-demand.v1.qos-status-changed" + time: '2024-06-01T13:00:00Z' + data: + sessionId: '123e4567-e89b-12d3-a456-426614174000' + qosStatus: 'UNAVAILABLE' + statusInfo: 'DURATION_EXPIRED' + + RETRIEVE_SESSIONS_EXAMPLE: + summary: List of QoS sessions for the specified device + description: A single QoS session for the specified device is available + value: + - applicationServer: + ipv4Address: 0.0.0.0/0 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + RETRIEVE_SESSIONS_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: List of QoS sessions for a specified device with the device in the response + description: A single QoS session for the device is available and the device to which the session applies is included in the response + value: + - device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 0.0.0.0/0 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 3600 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:00:00Z" + qosStatus: AVAILABLE + + SESSION_EXTENDED_EXAMPLE: + summary: Successful session extension with device not included in response + description: Example response after the duration of an active QoS session has been extended using a 3-legged access token, or possibly a single device identifier. The session remains AVAILABLE with updated duration and expiresAt values. + value: + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 5400 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:30:00Z" + qosStatus: AVAILABLE + + SESSION_EXTENDED_EXAMPLE_WITH_DEVICE_RESPONSE: + summary: Successful session extension with device included in response + description: Example response after the duration of an active QoS session has been extended using a 2-legged access token with multiple device identifiers, or possibly only a single device identifier. The session remains AVAILABLE with updated duration and expiresAt values. + value: + device: + phoneNumber: "+123456789" + applicationServer: + ipv4Address: 198.51.100.0/24 + qosProfile: QOS_L + sink: https://application-server.com/notifications + sessionId: 3fa85f64-5717-4562-b3fc-2c963f66afa6 + duration: 5400 + startedAt: "2024-06-01T12:00:00Z" + expiresAt: "2024-06-01T13:30:00Z" + qosStatus: AVAILABLE + + RETRIEVE_SESSIONS_EMPTY_EXAMPLE: + summary: No sessions found for the device + description: An empty array is returned when no sessions are found for the device + value: [] diff --git a/original/QualityOnDemand/documentation/API_documentation/QoD_User_Story.md b/original/QualityOnDemand/documentation/API_documentation/QoD_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..7596ab63f72103ffd33f61ffcc770a5f7566c253 --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/QoD_User_Story.md @@ -0,0 +1,10 @@ +# Quality-On-Demand (QoD) API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to request (using my application server/backend service), stable latency and/or stable throughput for a specified App-Flow from a Communication Service Provider (CSP), so that I can ensure better quality of experience for our end users including under network congestion. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:Developer
                                                              **Actors:** Application service providers, hyperscalers, application developers. This User Story does not explicitly describe consent management and hence end users are not included as Actors.
                                                              **Scope:** *Order To Activate (OTA)* \- Create/Remove/Get service instance (QoD session resource)\, get notification about the instance (QoD session resource) | +| ***Pre-conditions*** | The preconditions are listed below:
                                                              1. Customer:Developer is eligible to use the QoD API, i.e. the Customer has successfully subscribed to the QoD API on the platform of an API Provider
                                                              2. the customer application server has requested and received an access token for the required scopes of the API. Which specific authorization flows are to be used will be determined during onboarding process.
                                                              3. Optional: the customer application server has requested the list of available QoS Profiles with the qos-profile API (alternatively an upfront agreed QoS profile will be used)| +| ***Activities/Steps*** | **Starts when:** The customer application server makes a POST request to the QoD API to create a new QoD session resource with a specified duration and an available QoS Profile, and optionally registers a callback URL for receiving notification events.
                                                                **Ends when:** The customer application server makes a DELETE request to the QoD API, or the QoD session resource deletion was triggered automatically either because the set duration has expired or the session was terminated by the network (e.g. due to lack of resources). | +| ***Post-conditions*** | The specified App-Flow was provided stable latency or stable throughput and if callback URL was specified, a QoD session resource termination notification was received at the end. | +| ***Exceptions*** | Several exceptions might occur during the QoD API operations
                                                                - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                                                                - Conflict: Internal configuration policies didn’t allow for operations, e.g. a second QoD session for one device.
                                                                - Session-not-created: Due to other internal errors, QoS session resource could not be created| diff --git a/original/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table.md b/original/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table.md new file mode 100644 index 0000000000000000000000000000000000000000..227cede4b3bc8ab54e3b931d1e0dd69579b5042d --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/QoSProfile_Mapping_Table.md @@ -0,0 +1,16 @@ +# QoS Profiles Mapping Table (REFERENCE DRAFT) + +Here is one possible example of mapping table from QoS Profiles to provided connectivity characteristics. The intention of the examples is to illustrate the principle usage of the defined QoS Profile labels. It focus on connectivity characteristics in a wide area network usage. + +It is generally assumed that there exists an agreement between the API consumer and the API provider (e.g. a network operator or aggregator), which defines the service levels, conditions and restrictions. The agreement is not further detailed out here. In this sense the table below can be considered only as an example. + +## Example: Considering wide-area network usage. +| QOS Profile labels | Network Service Description | Network Service Constraints | +|----------| --------- | ----------- | +| QOS\_E | Latency stays stable under congestion (throughput up to a certain limit, e.g. 500kbps). The application bitrate should not exceed the limit. | The service is only provided, when the device is located within the geographical area, according to the agreement with the API provider.
                                                                The access to the network service is restricted to a maximal number of simultaneous session. | +| QOS\_L | The network throughput is prioritized up to certain higher limit (e.g. 20Mbps), or without an explicit limit. At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                                                                The access to the network service is restricted to a maximal number of simultaneous sessions. | +| QOS\_M | The network throughput is prioritized up to certain medium limit (e.g. 8Mbps). At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                                                                The access to the network service is restricted to a maximal number of simultaneous sessions. | +| QOS\_S | The network throughput is prioritized up to certain lower limit (e.g. 4Mbps). At high load, the throughput may be capped at the limit and can be degraded to lower effective throughput (without a minimum level). | The service is only provided, when the device is located within the home network.
                                                                The access to the network service is restricted to a maximal number of simultaneous session. | + +**Note:** +The QOS profile labels in the table can be used within Camara for validating the QoD APIs. diff --git a/original/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story.md b/original/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..42164563ee04553be373adf659f1e61fc9902c08 --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/QoSProfile_User_Story.md @@ -0,0 +1,10 @@ +# Quality-Of-Service-Profile (QoS Profile) User Story + +| **Item** | **Details** | +| ----------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **_Summary_** | As an application developer, I want to be able to query the list of available Quality of Service (QoS) profiles. I can then use use one of the Qos Profiles to start a Quality On Demand (QoD) session with a Communication Service Provider (CSP). The QoS profile contains information regarding network requirements for an application such as stable latency or throughput. | +| **_Roles, Actors and Scope_** | **Roles:** API Consumer:Developer

                                                                **Actors:** Application service providers, hyperscalers, application developers.

                                                                **Scope:**
                                                                • Retrieve a list of available QoS profiles (optionally filter by device)
                                                                • Get details of a QoS Profile
                                                                | +| **_Pre-conditions_** | The preconditions are listed below:
                                                                1. Customer:Developer is eligible to use the QoS Profile API, i.e. the Customer has successfully subscribed to the QoS Profile API on the platform of an API Provider
                                                                2. The customer application has requested and received an access token for the required scopes of the API. Which specific authorization flows are to be used will be determined during onboarding process.
                                                                | +| **_Activities/Steps_** | **Starts when:** The customer application either makes a POST to retrieve the list of available QoS Profiles or a GET to see the individual details of a QoS Profile.

                                                                **Ends when:** When the API Consumer:Developer identifies the QoS Profile to use when creating a QoD session. | +| **_Post-conditions_** | None - this is an immutable API. | +| **_Exceptions_** | Several exceptions might occur during the QoS Profile API operations
                                                                - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected). | diff --git a/original/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist.md b/original/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..43753ae14cc7d12799af4e888ca92dc3fc98670d --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/qos-profiles-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for qos-profiles v1.1.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                public | stable
                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qos-profiles.yaml](/code/API_definitions/qos-profiles.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline within YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/QoSProfile_User_Story.md](/documentation/API_documentation/QoSProfile_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see issue [#492](https://github.com/camaraproject/QualityOnDemand/issues/492) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/AYCtB) | + +(1) Multiple implementation by other operators of previous versions (source: https://open-gateway.gsma.com/map as of 2025-08-29). + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist.md b/original/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..6f121f2707ec9d2418677ecd6f293212febfcfdf --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/qos-provisioning-API-Readiness-Checklist.md @@ -0,0 +1,21 @@ +# API Readiness Checklist + +Checklist for qos-provisioning v0.3.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                public | stable
                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|------| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/qos-provisioning.yaml](/code/API_definitions/qos-provisioning.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/FYCtB) | + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist.md b/original/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..8448d3cebfbff28b7d36e0b63f6f4f9407d1e35d --- /dev/null +++ b/original/QualityOnDemand/documentation/API_documentation/quality-on-demand-API-Readiness-Checklist.md @@ -0,0 +1,23 @@ +# API Readiness Checklist + +Checklist for quality-on-demand v1.1.0 in r3.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                public | stable
                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|----| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/quality-on-demand.yaml](/code/API_definitions/quality-on-demand.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/QoD_User_Story.md](/documentation/API_documentation/QoD_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see issue [#493](https://github.com/camaraproject/QualityOnDemand/issues/493) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [/CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/9ACqB) | + +(1) Multiple implementation by other operators of previous versions (source: https://open-gateway.gsma.com/map as of 2025-08-29). + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021.md b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021.md new file mode 100644 index 0000000000000000000000000000000000000000..891a2b89f731b5436ffd187155ae66ff533b0022 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-10-12-2021.md @@ -0,0 +1,31 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 10-Dec-2021 + +## Attendees +- Joseantonio Ordonezlucena (Telefonica) +- Petar Torre (Intel) +- Ali Tizghadam (Telus) +- Toshi WAKAYAMA (KDDI) +- Jan Friman (E///) +- Emil Zhang (E///) +- Joachim Dahlgren (E///) +- Christoph Goertz (MobileEdgex) +- Mariusz Sozanski (DT) +- Felix DSouza (DT) +- Shilpa Padgaonkar (DT) + +## Goals +- Check when to restart meetings next year. +- Go through qod open issues +- Identify additional tasks, prepare upcoming ones + +Item | Description +---- | ---- +WG Meeting Series next year | Should be restarted after the first general alliance meeting planned for next year. Invites will follow +QoD open issue https://github.com/camaraproject/rep_main/issues/15 | E/// will provide an introduction to the 2 proposed specifications in the upcoming WG call and will provide details about additional features offered by the specs. They will also provide recmmendations/proposals if any features could be incorporated in existing APIs. +QoD open issue https://github.com/camaraproject/rep_main/issues/16 | All issues were discussed and clarified. We have following action items from the issue discussions:-
                                                                • Userstories behind qod apis will be submitted by DT in the userstory template format approved from the commonalities WG
                                                                • Stable vs guaranteed more details from DT to follow in one of the next calls
                                                                •The term Appflow might limit further possibilities(UE-UE)flow if the API scope is extended later, but we agree to keep it as is currently and can change it if needed in future. Standard resource document in commonalities WG can address the vocabalary consistency issue.
                                                                • Subactivity to discuss which notificiations are relevant for the QoD API family. Add your insights here:- https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md
                                                                • Alternatives requested for "session" 2 suggestions already provided by E/// . Alternatives can be documented here https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Changes.md +QoD open issue https://github.com/camaraproject/rep_main/issues/18 | All issues were discussed and clarified. Some action items for DT:-
                                                                • Provide details what would differ in future regarding the 2 APIs which drove the decision to split the APIs in two
                                                                • What happens when consumer needs combination of both?
                                                                • Can the API be extended to provide the consumer with available profile options? + + + diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021.md b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021.md new file mode 100644 index 0000000000000000000000000000000000000000..683611751d75c95e0cd3f992b3d0b90c218dbe35 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-22-10-2021.md @@ -0,0 +1,30 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 22-Oct-2021 +**Note Taker:** Shilpa Padgaonkar + +## Attendees +- Petar Torre +- Joseantonio Ordonezlucena +- Ali Tizghadam +- Noel Wirzius +- Shilpa Padgaonkar + +## Goals +- Workstream1 Kickoff +- Introductions +- Identify additional tasks, prepare upcoming ones + +## Agenda Items + +Item | Description +---- | ---- +Regular meeting schedule | • Agreed to have bi-weekly calls
                                                                • Shilpa will send out doodle pool for regular bi-weekly time slots +Contributions| • **Intel**
                                                                - **Supporting capability NEF (Rel-15) sample code:** Intel Distribution of OpenNESS (requires Intel license) has sample application for Network Exposure Function (summary in , API spec here). With support to integrate above NEF sample code.(eg. provide mock code for subset of NEF features)
                                                                - **Kubernetes and Telemetry:** (Assuming use of Kubernetes) Activate Kubernetes features useful for optimal workload placement (CPU Mgr…), and possibly platform telemetry supporting “to get notification if network cannot fulfill”.  (eg. Scheduling, notifications specific contributions)
                                                                - **e2e performance characterization:** If during the integration of such API, exposure gateway, NFs… you plan to do performance characterization, we might help with people experienced in similar characterization focusing on edge workloads. (eg. testing framworks, tools, testcases)
                                                                - **Documenting API design principles:** Contribute text on API design principles like “must Encapsulate; should be Declarative”, with Terminology/Glossary as needed. 

                                                                • **Telefonica**
                                                                - Define userstories and usecases
                                                                - Analyse set of existing APIs and capabilities and how to enrich them
                                                                - Offer to validate the APIs contributed to the project by using a self built validation tool
                                                                - Test cases 

                                                                • **Telus**
                                                                - Offer to validate the APIs contributed to the project
                                                                - Test cases
                                                                - Will try to contribute for API development 

                                                                • **DT**
                                                                - API specs
                                                                - Reference implementation for some of the APIs
                                                                - Test cases
                                                                - Validation of APIs
                                                                +Topics for Commonality Workstream| • API Spec format
                                                                • Authentication and Authorization
                                                                • Should tools for telemetry/scheduling/performance characterizations be based on a technology like Kubernetes?
                                                                • Use of Intel's OpeNESS platform
                                                                • Recommended tools for testcases + + + + +## Other Notes +N/A diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021.md b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021.md new file mode 100644 index 0000000000000000000000000000000000000000..2228022b71030119f2dd3562b63c9938d6c03e3e --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2021/MOM-26-11-2021.md @@ -0,0 +1,28 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 26-Nov-2021 + +## Attendees +- Jan Friman +- Joachim Dahlgren +- Petar Torre +- Ali Tizghadam +- Felix Dsouza +- Mariusz Sozanski + + +## Goals +- Recap +- Update on API specs +- Q&A + +## Agenda Items + +Item | Description +---- | ---- +Recap | During the last meeting an update of the Quality on Demand APIs have been announced.
                                                                The API specs have been published last week. Last meeting's presentation slides have been published at https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/documentation/Presentations/QoD-API_Alliance.pdf +Update on API specs | • The updated API specs are now available at https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand
                                                                • The specs version is now "stable": it won't be altered within the next 2 months to provide a stable basis for initial testing by developers.
                                                                • All feedback, comments and proposals are welcome! +Q&A | • **Why two similar separate APIs have been created instead of a single one with two features?**
                                                                   We wanted to make things as simple as possible. Although (in fact) currently there is just one common testing API behind, in the future the two QoD may diverge significantly, thus it has been decided to keep them separated. Still, this may be revised later on in further development. + +## Request to participants + • **Any feedback on the current API specs will be appreciated, thank you!**
                                                                diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21.md new file mode 100644 index 0000000000000000000000000000000000000000..a84b940ace67f965c045199c3a2202efa1283841 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-01-21.md @@ -0,0 +1,28 @@ +# Meeting Minutes +## Meeting Information +**Meeting Date:** 21-Jan-2022 + +## Attendees +- Petar Torre (Intel) +- Ali Tizghadam (Telus) +- Toshi WAKAYAMA (KDDI) +- Jan Friman (E///) +- Emil Zhang (E///) +- Joachim Dahlgren (E///) +- Christoph Goertz (MobileEdgex) +- Mariusz Sozanski (DT) +- Noel Wirzius (DT) +- Steffen Drüsedow (DT) +- Shilpa Padgaonkar (DT) + +## Goals +Go through last MoM action items +Identify additional tasks, prepare upcoming ones + +Item | Who | Description +---- | ---- | ---- +Open questions from last WG call:
                                                                • Provide details what would differ in future regarding the 2 APIs
                                                                • What happens when consumer needs combination of both?
                                                                •Api to provide the consumer with available profile options | DT | Issue has been updated with answers as latest comments #16 +Issue15
                                                                •Consider additional specs | E/// |•Emil will prepare the presentation and inform when it needs to be part of hte agenda.
                                                                •Part of the requirements were presented to the bigger Camara group https://github.com/camaraproject/rep_main/blob/main/WorkingGroups/Commonalities/Camara%20assumptions%20and%20missing%20concepts.pdf. +Issue18
                                                                •Subactivity to create table to map ‘Throughput_S/M/L’ and ‘LOW_LATENCY’ and standard 3GPP QCI/5QI values. | Telefonica | Doc yet to be created +Split E/// proposals into 3 separate issues:-
                                                                • GPSI as UE identifier under general label so that wider audience get a say and is not limited to WG members only
                                                                • Document common terminologies and vocabulary across API families to use issue to be checked with commonalities gruop if it can be addresses by resource description doc and E/// will help in partly contributing to the doc
                                                                • Authorization related issue should be also under commonalities WG|All | E/// will create the 3 separate issues and add appropriate labels for the same +New issue will be created under QoD WG to explain the impact of possible UE authorization on the current QoD API spec |DT, E/// | E/// will document as comments to this issue how the API would change if checks for authorized UE were to be in scope. https://github.com/camaraproject/rep_main/issues/34 diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04.md new file mode 100644 index 0000000000000000000000000000000000000000..3c814ad709eefa61a917d54c68a107b66c88007d --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-04.md @@ -0,0 +1,32 @@ +# Camara QoD meeting +### Date: 04 Feb 2022 + +## Attendees +- **_Ali Tizghadam (Telus)_** +- **_Jose Antonio Ordonez Lucena (TEF)_** +- **_Sylvain Morel (Orange)_** +- **_Toshi WAKAYAMA (KDDI)_** +- **_Jan Friman (E///)_** +- _**Joachim Dahlgren (E///**)_ +- **_Francesc Guim (Intel)_** +- **_Steffen Drüsedow(DT)_** +- **_Shilpa Padgaonkar (DT)_** +- **_Marcin Jarzab (DT)_** + +All QoD minutes link: [https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes](https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes) + +## Goals +- Go through last MoM action items +- Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items +Agenda Item | Who|   +---- | -------- | ---- +Welcome & Recap |  |- Api specs are available at:
                                                                [https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand](https://github.com/camaraproject/rep_main/tree/main/APIs/QualityOnDemand)

                                                                - Reviews from WG members discussed and worked on using open issues: [https://github.com/camaraproject/rep_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD](https://github.com/camaraproject/rep_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD)

                                                                - E/// proposals in issue #33 have been split into 4 separate issues (#34 and #36-38):
                                                                   1. Impact of verification for authorised recipient (e.g. UE) on QoD API spec (issue #34)
                                                                   2. GPSI as UE identifier under _general_ label so that wider audience get a say
                                                                   3. Terminology related issue merged with #24 in _commonalities_ group
                                                                   4. Authorisation related issue also under _commonalities

                                                                - topics started to be addressed within relevant GitHub issues - thanks! +Issue #15
                                                                Consider additional specs: more network API specifications which have QoS support beyond the well-known NEF APIs| E/// |
                                                                - E/// is working on new presentation to provide details for extension/changes proposed for issue #15
                                                                - Proposal to make this a Camara medium-term objective by DT & TEF while waiting for EES/SEAL implementations.
                                                                - This issue is being marked as QoD-backlog = this is a new label for postponing issues as keeping as backlog +Issue #16
                                                                Questions on QoD user stories | E///|- new comments (TEF): We should follow user story template discussed in Commonalities WG for every selected use case. Otherwise, some of the details/implications of the user stories are not fully clear.
                                                                - Issue to be closed and re-opened upon completion of Commonalities User Stories template +Issue #18
                                                                Subactivity to create table to map ‘Throughput_S/M/L’ and ‘LOW_LATENCY’ and standard 3GPP QCI/5QI values. |Telefónica|- questions 1&2 addressed in December.
                                                                - Question 3: table mapping activity created as issue #21
                                                                - to be closed as soon as #21 is developed +Issue #19 & #20 are _enhancements_
                                                                - Add possibility to specify duration in the QoD APIs
                                                                - Add new endpoint in QoD API to request available qos_profiles| DT | Issue #19 is under development (DT):
                                                                - it is not going to be a mandatory feature
                                                                - An example of B2C "boost activation" use case could be gaming apps (a specific use case may be described in more detail during one of next meetings)
                                                                - Orange: monitoring of duration and consumption and complementary offer of QoS linked to specific area could be proposed as further enhancement
                                                                - TEF: this feature will simplify the API consumer life so he does not have to remember to deactivate. But more background functions may be needed for the implementation, therefore implications of what is to be included (e.g. a duration timer) should be analyzed

                                                                Issue #20 will be labeled as QoD-backlog due to other on-going priorities
                                                                - the operation is going to be performed through discovery +Issue #21
                                                                Create a mapping table for qos_profiles |All |Everyone is invited to contribute and add proposed rows to the table. The draft placeholder is located under: [https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/QoSProfile_Mapping_Table.md](https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/QoSProfile_Mapping_Table.md) +Issue #22
                                                                Document relevant notifications for QoD APIs|All| A placeholder for the list of notifications (e.g. _session_termination_ notification) relevant for the QoD API family has been created: [https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md](https://github.com/camaraproject/rep_main/blob/main/APIs/QualityOnDemand/Notifications.md)
                                                                Everyone is invited to contribute to the newly created table. +Issue #34
                                                                impact of verification for authorised recipient (e.g. UE) on API spec | E/// | issue #36 outcome can impact the QoD API (e.g. GPSI id vs IP identification). Using NEF could be possible to have a translation - to be addressed in #36. diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18.md new file mode 100644 index 0000000000000000000000000000000000000000..907edd0256ac1334473b98a71b69fe4cab3f785e --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-02-18.md @@ -0,0 +1,44 @@ +# Camara QoD meeting + +### Date: 18 Feb 2022 + +## Attendees + +* *Petar Torre (Intel)* +* *Thomas Vits (TangibleXR)* +* *Jose Antonio Ordonez Lucena (TEF)* +* *Toshi WAKAYAMA (KDDI)* +* *Jan Friman (E///)* +* *Emil Zhang (E///)* +* *Christoph Goertz (MobileEdgex)* +* *Marcin Jarzab (DT)* + +All QoD minutes link: [https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes](https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand/documentation/MeetingMinutes) + +## Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| Welcome & Recap | | \- New API version 1\.2\.0 specs are available at:
                                                                [https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand](https://github.com/camaraproject/rep\_main/tree/main/APIs/QualityOnDemand)
                                                                \- Reviews from WG members discussed and worked on using open issues: [https://github.com/camaraproject/rep\_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD](https://github.com/camaraproject/rep\_main/issues?q=is%3Aissue+is%3Aopen+label%3AQoD)
                                                                \- topics started to be addressed within relevant GitHub issues \- thanks\! | +| | | | +| *CLOSED ISSUES* | | | +| Issue #19: **closed**
                                                                \- Add possibility to specify duration in the QoD APIs | DT | [Issue #19](https://github.com/camaraproject/rep\_main/issues/19) has been addressed:
                                                                \- version 1\.2\.0 of the API definitions uploaded to *QualityOnDemand* subdirectory.
                                                                The new version implements the duration parameter of *CreateSession* component schema and a *SESSION\_TERMINATED* event when the session ends/expires.
                                                                \- The duration property is not going to be a mandatory parameter and is defined as follows:
                                                                *`(...)`*
                                                                `duration:`
                                                                ` type: integer`
                                                                ` example: 86400`
                                                                ` description: `
                                                                `____Session duration in seconds. Maximal value of 24 hours is used if not set.`
                                                                `____After session has expired the client will receive SESSION_TERMINATED event. See`
                                                                `____notification callback.`
                                                                ` format: int32`
                                                                ` minimum: 1`
                                                                ` maximum: 86400`
                                                                *`(...)`* | +| Issue #16 **closed**
                                                                Questions on QoD user stories | E/// | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.
                                                                \- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template | +| Issue #18 **closed**
                                                                Subactivity to create table to map ‘Throughput\_S/M/L’ and ‘LOW\_LATENCY’ and standard 3GPP QCI/5QI values. | Telefónica | \- questions 1&2 addressed in December\.
                                                                \- Question 3: table mapping activity created as issue \#21 in order to close this issue\. | +| | | | +| *CURRENT ISSUES* | | | +| Issue #21
                                                                Create a mapping table for qos\_profiles | TEF/DT? | The draft placeholder is located under: [https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/QoSProfile\_Mapping\_Table.md)
                                                                \* DT: There are multiple values of QCI/5QI to be mapped: configuration blueprint to be done by API vendor
                                                                \* TangibleXR: a possible workaround is API Discovery; the parameter options would be explained in API and translated into proper values. Defining normative values may not be in scope of Camara (but rather reserved for each business/CSP on their own)
                                                                \* TEF: then a problem arises with consistency and providing quality of UX. There are plenty of options, but to ensure consistent testing, we need a ref. value from each tag.
                                                                \* We agree to create an initial blueprint draft, possibly created by TEF (and DT co-operation) to put this discussion further and see if we can create a commonly accepted document | +| Issue #22
                                                                Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created: [https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/Notifications.md](https://github.com/camaraproject/rep\_main/blob/main/APIs/QualityOnDemand/Notifications.md)
                                                                \* currently only *session\_termination* notification is present
                                                                \* please document which other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue #15
                                                                Consider additional specs: more network API specifications which have QoS support beyond the well-known NEF APIs | E/// | \* to be closed following contribution by E/// to Camara - being investigated by Commonalities group
                                                                \* update coming in GitHub next week before the Camara Commonalities group meeting so it can be discussed then | +| Issue #20: *enhancement*
                                                                \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #20 will be labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery | +| Issue #34
                                                                impact of verification for authorised recipient (e.g. UE) on API spec | E/// | issue #36 outcome can impact the QoD API (e.g. GPSI id vs IP identification). Using NEF could be possible to have a translation - to be addressed in #36. | +| | | | +| AOB | | | +| | | 1\. Next QoD meeting in two weeks on the 4th of March\.
                                                                2\. OPAG GSMA is interested in collaboration\, a\.o\. in QoD specification\. | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04.md new file mode 100644 index 0000000000000000000000000000000000000000..cbb53522770598b1390e4370e340d6c9a6dc1952 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-04.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 4 Mar 2022 + +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Attendees + +* **Jose Antonio Ordonez Lucena (TEF)** +* **Petar Torre (Intel)** +* **Ali Tizghadam (Telus)** +* **Andrew Wajs (Scenera)** +* **Sylvain Morel (Orange)** +* **Toshi WAKAYAMA (KDDI)** +* **Jan Friman (E///)** +* **Emil Zhang (E///)** +* **Joachim Dahlgren (E///)** +* **Shilpa Padgaonkar (DT)** +* **Slawomir Tkacz (DT)** + + +### Goals + +* Go through issues/action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Camara announced at MWC 2022.
                                                                **NEW** repository structure:
                                                                \* the steering committee decided to move the working groups and QoD API subproject to separate repositories
                                                                \* new QoD repo address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                \* new organisation of directories | +| | | \- API version 1\.2\.0 \(see also new Commonalities [issue #25](https://github.com/camaraproject/WorkingGroups/issues/25)) specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue #21 -> QoD#1
                                                                Create a mapping table for qos\_profiles | TEF/DT/
                                                                /All? | The draft placeholder has been relocated to:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                                                                \* Multiple values of QCI/5QI to be mapped, possibly via a configuration blueprint

                                                                \* TEF: 5QI initial investigation by TEF leads to suggest to limit the throughput to two values: standard and premium for validation purposes. At least as internal reference validation for Camara.
                                                                \* standard NEST for eMBB slice -> 3GPP 5QI: 1,2,5,6,7,8,9

                                                                \* Orange: Maybe a range of values possible for operators to choose could be possible.
                                                                \* DT: could we leave this to operators, so they can customize their offering (as, e.g., cloud operators do).
                                                                \* Intel: we need to guarantee consistency towards developers by offering at least similar values.

                                                                \* TODO actions:
                                                                \- please reflect your proposals/comments under [GitHub issue #1](https://github.com/camaraproject/QualityOnDemand/issues/1)
                                                                \- check internally with teams what has been tested/proposed | +| Issue #22 -> QoD#2
                                                                Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                                                                \* currently only *session\_termination* notification is present

                                                                \* E///: add QoS monitoring event notifications from NEF - it may be a candidate for future notification
                                                                \* DT: we were not able to validate other notifications internally until now
                                                                \* Orange: specific feedback on QoS event, tested in Orange, to be discussed internally if other notifications are relevant

                                                                \* TODO: please document through the [GitHub issue](https://github.com/camaraproject/QualityOnDemand/issues/2) if other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue #15 -> #6
                                                                Consider more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                                                                \* consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog. | +| Issue #20 -> #7
                                                                \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) will be labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery | +| Issue #34 -> #8
                                                                impact of verification for authorised recipient (e.g. UE) on API spec | E/// | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC. | +| Issue #16 / #3 *closed*
                                                                Update of QoD user stories | E/// | \- We should follow user story template discussed in Commonalities WG for every selected use case\.
                                                                \- Issue has been closed \- QoD user stories will be updated upon completion of Commonalities User Stories template\. | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 18th of March\. | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18.md new file mode 100644 index 0000000000000000000000000000000000000000..51356c84291c256fac4028d1083bb093099dfaee --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-03-18.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 18 Mar 2022 + +## Attendees + +* **Petar Torre (Intel)** +* **Cesc Guim (Intel)** +* **Toshi WAKAYAMA (KDDI)** +* **Jan Friman (E///)** +* **Emil Zhang (E///)** +* **Joachim Dahlgren (E///)** +* **Eric Murray (Vodafone)** +* **Kevin Smith (Vodafone)** +* **Ivan Nieto (Vodafone)** +* **Steffen Drüsedow (DT)** +* **Marcin Jarząb (DT)** + +
                                                                +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | **NEW** repository structure:
                                                                \* the steering committee decided to move the working groups and QOD API subproject to separate repositories
                                                                \* new QoD repo address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                \* new organisation of directories | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue QoD#1
                                                                Create a mapping table for qos\_profiles | TEF/DT? | A reference draft has for discussion been published to:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                                                                \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                                                                \* ToDO: please verify and comment through the GITHUB ISSUE your position on such mapping
                                                                \* change L to "up to unlimited" proposal as in Vodafone e.g. | +| Issue QoD#2
                                                                Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                                                                \* currently only *session\_termination* notification is present
                                                                \* ToDo: please document through issue if other notification may be relevant for the Service API | +| | | | +| *QOD-BACKLOG* | | | +| Issue QoD#3 Questions on QoD user stories | DT | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.\- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template next week \(TODO\) | +| Issue #6
                                                                Consider additional specs: more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                                                                consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog.
                                                                \* ToDo: to be closed as the UEid has been proposed. | +| Issue #7
                                                                \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) will be labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery | +| Issue #8
                                                                impact of verification for authorised recipient (e.g. UE) on API spec | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                                                                \* todo: please comment in the issue
                                                                \* the auth by GPSI is initially accepted by the workgroup - still, the impact on API def is to be analyzed | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 1st of April\. | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01.md new file mode 100644 index 0000000000000000000000000000000000000000..36018e14a3adecbb6eba4a9ec8f3286c8420bf33 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-01.md @@ -0,0 +1,56 @@ +# Camara QoD meeting + +### Date: 1st of April 2022 + +## Attendees + +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** +* ***Tomas Vits (MobiledgeX)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** + +
                                                                + +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| | | | +| **CURRENT ISSUES** | | | +| Issue QoD#1
                                                                Create a mapping table for qos\_profiles | TEF/DT | A reference draft has for discussion been published to:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                                                                \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                                                                \* change L to "up to unlimited" or rather "best effort" (Vodafone proposal), see [GitHub comment](https://github.com/camaraproject/QualityOnDemand/issues/1)
                                                                \* DT agrees with Vodafone comments and notes that it this mapping table is just an example that could be used for validations within the alliance. 
                                                                \* Orange: Maintaining a separate YAML for every new profile is not manageable and this could instead be delegated to the discovery service as specified in issue #7
                                                                \* DT:  The discovery API is in our backlog and once implemented, the separate YAML constructs wont be needed anymore.
                                                                \* ToDO: please verify and comment through the GitHub ISSUE your position on such mapping | +| Issue QoD#2
                                                                Document relevant notifications for QoD APIs | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                                                                \* currently only *session\_termination* notification is present | +| Issue QoD#9
                                                                security requirements bug | DT | \* corrected security requirements mistake/"typo" (referring to *APIKeys* instead of *oAuth2ClientCredentials*) with PR#10
                                                                \* Orange is working on a possible real-life implementation. Lab with E/// SCEF, checking both radio access types.
                                                                \* DT: working as well on NEF.
                                                                -> We could validate it in both cases, hoping to validate it additionally with a NEF emulator.
                                                                \* Intel prepared a NEF emulator, investigating internally on its capabilities ([Commonalities issue #26](https://github.com/camaraproject/WorkingGroups/issues/26)). | +| NEW TOPIC | Orange | \* Orange Q: If an API such as the one used for QoD could be applied for both 4G/5G, what should be the validation process? 
                                                                DT-> This question  could be valid for more than just the QoD API and a new issue in commonalities will be created to discuss the details.
                                                                ToDo: create issue in  commonalities issue for verification of API 4G/5G capabilities

                                                                Orange: We wish to provide reference implementation of QoD APIs and validate it against SCEF. Would be interested in alignment with other partners on this. 
                                                                DT: working on implementation as well and will validate against NEF. Another validation will be mostly don't against NEF emulator contributed to community (possibly from Intel) | +| | | | +| *QOD-BACKLOG* | | | +| Issue QoD#3 Questions on QoD user stories | DT | \- comment from TEF under the GitHub issue: We should follow user story template discussed in Commonalities WG for every selected use case\.
                                                                \- Issue has been closed \- to be re\-opened upon completion of Commonalities User Stories template next week
                                                                ToDo:
                                                                \* Open new issue to contribute user stories based on template
                                                                \* Open another issue to contribute api documentation based on template | +| Issue #6
                                                                Consider additional specs: more network API specifications | E/// | Issue #6 - consider more network API specifications which have QoS support beyond the well-known NEF APIs
                                                                consider EES/SEAL also within CAMARA scope, but maybe as medium-term objective in the backlog.
                                                                \* DT: related to GPSI GH issue on Commonalities
                                                                \* E/// closed this issue, please see related [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4) for further comments and discussion. | +| Issue #7
                                                                \- Add new endpoint in QoD API to request available qos\_profiles | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1)) | +| Issue #8
                                                                impact of verification for authorised recipient (e.g. UE) on API spec | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4): the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx)   to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                                                                * the auth by GPSI is initially accepted by the workgroup - still, the impact on API def is to be analyzed
                                                                * thank you for comments in the issue | +| | | | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 22nd of April\. | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22.md new file mode 100644 index 0000000000000000000000000000000000000000..d303f4ff7b2a9142bf9af83618ea2da166a691f1 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-04-22.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +### Date: 22nd of April 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** + +
                                                                +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 6 , Closed: 5 ]** | +| Issue QoD#1
                                                                *Create a mapping table for qos\_profiles* | TEF/DT | A reference draft has for discussion been published to:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/QoSProfile_Mapping_Table.md)
                                                                \* **Note**: This table is only an example that can be used within Camara for validating the QoD APIs
                                                                \* change L to "up to unlimited" or rather "best effort" (Vodafone proposal), see [GitHub comment](https://github.com/camaraproject/QualityOnDemand/issues/1)
                                                                \* DT agrees with Vodafone comments and notes that it this mapping table is just an example that could be used for validations within the alliance. 
                                                                \* Orange: Maintaining a separate YAML for every new profile is not manageable and this could instead be delegated to the discovery service as specified in issue #7
                                                                \* DT:  The discovery API is in our backlog and once implemented, the separate YAML constructs wont be needed anymore.
                                                                \* ToDO: please verify and comment through the GitHub ISSUE your position on such mapping
                                                                **Status : Open/Active discussion**  
                                                                **Proposed action: Close** | +| Issue QoD#2
                                                                *Document relevant notifications for QoD APIs* | All | A placeholder for the list of notifications (e.g. *session\_termination* notification) relevant for the QoD API family has been created:
                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/code/API\_definitions/Notifications.md](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/Notifications.md)
                                                                \* currently only *session\_termination* notification is present
                                                                **Status : Open/Active**
                                                                **Proposed action : Closed (Comment: Issue closed with Living document only)** | +| Issue QoD#12
                                                                *Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template
                                                                \* *DT is working internally (DOC internal review)*
                                                                **Status : Open/Active** | +| **NEW Topic** | | | +| Issue #11
                                                                *\- Is enum the best choice for qos\_profile* | Orange | -What if a client needs a QoS profile with LOW\_LATENCY and THROUGHPUT\_L?
                                                                -We would need to add an enum key that represents this combination and also a new key for all other relevant ones.
                                                                -We could associate each profile with values based on the power of two (1, 2, 4, 8, 16...) and compose them via an OR operation. 
                                                                *DT comment:*
                                                                -CAMARA goal is to define some general approach -> production deployments will differ 
                                                                -Discovery profile API might be solution to get list of QOS Profile "flavours"
                                                                -Simmilar approach applied by Public cloud vendors (Instance flavours for many use-cases)
                                                                -Will depend on Operator and Technology (e.g. GSMA based blueprint possible)
                                                                **Status: Open/Discussion started**
                                                                **Proposed action: Close (?) or just propose more details regarding the requirement** | +| **QoD Backlog** | | | +| Issue #7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))
                                                                \* DT will check internaly with DEV team | +| Issue #8
                                                                *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4):
                                                                the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                                                                \* the auth by GPSI is initially accepted by the workgroup - still, **the impact on API def is to be analyzed**
                                                                \* technical discussion on-going (include Commonalities) : Security and Auth will not be part of API
                                                                \* E/// proposed to close
                                                                **Status: Open/Active discussion**
                                                                **Proposed action: Continue effort (define user stories and design)** 
                                                                   **->Organize global meeting to discuss within broader audience (@M.K)** | +| **AOB** | | | +| | | 1\. GSMA OPG/OPAG expressed interest in collaboration with CAMARA project
                                                                  \* *QoS/NW Events/Mobility and others are on PRIO list (SBI-NR 3GPP API list) : CAMARA alligment is being discussed* 
                                                                  \* EDGE API contribution diccussed      
                                                                2\. Next QoD meeting in two weeks on the 6th of May\.
                                                                3\. Patrice@Orange \- Notifications / Authentications on server side
                                                                  -> Have owners of security topic and prepare dedicated technical meeting (related to #8) | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06.md new file mode 100644 index 0000000000000000000000000000000000000000..fb1cedca6817aa71cad49b433436ba61fb45fc75 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-06.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +### Date: 6-th of May 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Mariusz Sozanski (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Shilpa Padgaonkar (DT)*** +* ***Petar Torre (Intel)*** +* ***Francesc Guim (Intel)*** +* ***Ali Tizghadam (Telus)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Eric Murray (Vodafone)*** +* ***Ivan Nieto (Vodafone)*** +* ***Andrew Wajs (Scenera)*** + +
                                                                +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 3 , Closed: 8 ]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template
                                                                \* *DT is working internally (DOC internal review)*
                                                                **Status : Open/Active development \* Update : User stories and API-docs under internal review in DT** | +| Issue #7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))
                                                                **Status : Open/Active development**
                                                                \* DT will check internaly with DEV team -> **agreed and defined within "current" Sprint scope**
                                                                **\* Activity started and "internal" proposal being discussed : *(on-going activity)*** | +| **NEW ISSUES** | | | +| *Issue not assigned ID*
                                                                -Notifications / Authentications on server side | Orange | Patrice@Orange - Notifications / Authentications on server side
                                                                 \* Have owners of security topic and prepare dedicated technical meeting (related to #8)
                                                                 \* *Topic to be discussed within Commonalities group (TBC)* | +| Testing and Validation | DT,
                                                                Orange | \* we need to start to summary leassons learnt from Dev/Validate   
                                                                \* pririties on validation , make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT internal solution TBC  
                                                                  -> what is the requirement / QoS profiles : on-demand resource reservation and numbers 
                                                                    UPlink flow for Video/Control function 
                                                                    based on the solution definition of testing requirments would be easier to define and understand 
                                                                \* Orange 
                                                                  conditions in which API is called etc
                                                                   ->  will prepare some short material  | +| Transform Function | TEF | Goal : Service API will deliver consistent funcionality for End-users
                                                                \- Metrics names and target goals 
                                                                \- How to include into Transform Function 
                                                                \- testing workflow defined and included: CAMARA API / Transform / NEF 
                                                                -> short overview of idea be prepared by TEF | +| **QoD Backlog** | | | +| Issue #8
                                                                *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4):
                                                                the [proposal](https://github.com/camaraproject/WorkingGroups/blob/main/Commonalities/documentation/Deliverables/UE%20identifiers.pptx) to identify UEs primarily with GPSI (in any existing format either MSISDN or ext identifier) and optionally with UE IP or MAC.
                                                                \* the auth by GPSI is initially accepted by the workgroup - still, **the impact on API def is to be analyzed**
                                                                \* technical discussion on-going (include Commonalities) : Security and Auth will not be part of API
                                                                \* E/// proposed to close *(Confirmed during the meeting)*
                                                                **Status: Open/Active discussion -> Close (@Eric)** | +| **AOB** | | | +| | | 1\. Organization of QoD community \(R&D improvements\)
                                                                  \* GSMA OPAG/OPG collaboration / contribution still being discussed       
                                                                2\. Next QoD meeting in two weeks on the 20th of May\. | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20.md new file mode 100644 index 0000000000000000000000000000000000000000..c86005d9792b2b2bd6072036c0c73c6c48455640 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-05-20.md @@ -0,0 +1,44 @@ +# Camara QoD meeting + +### Date: 20th of May 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Jose Antonio Ordonez Lucena (TEF)*** +* ***Sylvain Morel (Orange)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** + +
                                                                +**NEW address:** All QoD minutes link: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 2 , Closed: 9 ]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template

                                                                **Status : Open/Active development *(under-review)***   
                                                                 **- UPDATE : User story and Latency/Bandwidth API-docs under internal review** | +| Issue #7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                                                                **Status : On-Hold**
                                                                **\* Activity started and "internal" proposal being discussed**
                                                                 **\- UPDATE : Discussed use cases \(e\.g\. Network Slice\) include feedback from Hyprescalers \- under consideration** | +| **NEW ISSUES** | | | +| Testing and Validation | DT,
                                                                Orange | \* We need to start to summary leassons learnt from Dev/Validate   
                                                                \* Priorities on validation, make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT internal solution (**TBC**)  
                                                                   - QoS profiles: what is the requirement  
                                                                   - On-demand resource reservation and numbers for UL/DL flows
                                                                   - Testing requirements would be easier to define and understand 
                                                                   - Example: Video/Control function based on the solution definition. 
                                                                   **UPDATE (DT/BMW/Valeo AVP):** 
                                                                    [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                                                                    - The data packets are transferred with always the same delay even under high load conditions (stable low latency) or           the bandwidth is kept on the same level even under high load (stable bandwidth).
                                                                    - During the time of the car maneuvering the data connection is prioritized against other data connections in the same         mobile cell.
                                                                    
                                                                *\* Example sequence diagram is requested with call flows    (Terminal -> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction )*     SeNF - Service Enabling Network Function 
                                                                ***\* Sample application to be considered***
                                                                    
                                                                \* Orange : conditions in which API is called
                                                                   -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                                                                \* Metrics names and target goals 
                                                                \* How to include into Transform Function 
                                                                \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                                                                **Transform Function**       
                                                                \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                                                                *\- Focus on 3GPP *& CAMARA* API with Mappping Table presented (PPT will be distributed)* | +| **QoD & API Backlogs** | | | +| Issue #8
                                                                *-Impact of verification for authorised recipient (e.g. UE) on API spec* | All | Issue #8 outcome can impact the QoD API (e.g. GPSI id vs IP identification).
                                                                This may be also loosely related to Commonalities Authentication & Authorization standards and [Commonalities issue #4](https://github.com/camaraproject/WorkingGroups/issues/4)
                                                                **Status: Closed** | +| API Backlog : 

                                                                Issue #29
                                                                - API to Request the Status of the Network Traffic   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                                                                When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 
                                                                \* Trade off between video quality and delay. If the delay reaches a threshold it is more desirable to reduce video quality than to have the highest possible video quality. It is desirable to reduce the video quality if it reduces the network delay for the video delivery.
                                                                \* Monitor API which provides an indication of the status of the network (delay and traffic levels and other parameters that would indicate the performance of the network).
                                                                \* Based on the status,the Application adjusts the encoding level to best suite the condition in network. 

                                                                **Status: Open / Discussed** 
                                                                \* QoD related topic are discussed 
                                                                 - Monitor API and Manage the "parameters" 
                                                                 - QoD members are encouraged to partcipate in the discussion
                                                                 - Let's discuss on the next meeting | +| **AOB** | | | +| | | 1\. GSMA OPG/OPAG Meetings \[24\-25\.05\] 
                                                                  \* Encouraged F2F Internal meetings to discuss issues & ideas        
                                                                2\. Next QoD meeting in two weeks on the 3rd of June | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03.md new file mode 100644 index 0000000000000000000000000000000000000000..ec82c800175adfd6d8ad705031048dda17f532da --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-03.md @@ -0,0 +1,43 @@ +# Camara QoD meeting + +### Date: 3rd of June 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** +* ***Tuan Tran (Broadpeak)*** +* ***Assane Niang (Orange)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 11 [ Open: 2 , Closed: 9 ]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template

                                                                Status : Open/Active DEV *(Under-review /* **No-Change )** | +| Issue QoD#7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                                                                **Status : On-Hold (No-Change)** | +| **NEW ISSUES / Discuss point** | | | +| Testing and Validation | DT,
                                                                Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                                                                \* Priorities on validation, make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT solution developed with partners: AVP sample application presented
                                                                    [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                                                                 *\- Following components discussed based on the AVP        Terminal \-> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                                                                     \* SeNF - Service Enabling Network Function 
                                                                   AVP Use case with Camara QoD description:
                                                                   [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                                                                   
                                                                   -> M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)

                                                                \* Orange : conditions in which API is called
                                                                 -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                                                                \* Metrics names and target goals 
                                                                \* How to include into Transform Function 
                                                                \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                                                                **Transform Function**       
                                                                \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                                                                *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                                                                - **On-going action proposed : How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management** 
                                                                 **-> Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **QoD & API Backlogs** | | | +| API Backlog : 

                                                                Issue #29
                                                                - API to Request the Status of the Network Traffic   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                                                                When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 
                                                                \* Trade off between video quality and delay. If the delay reaches a threshold it is more desirable to reduce video quality than to have the highest possible video quality. It is desirable to reduce the video quality if it reduces the network delay for the video delivery.
                                                                \* Monitor API which provides an indication of the status of the network (delay and traffic levels and other parameters that would indicate the performance of the network).
                                                                \* Based on the status,the Application adjusts the encoding level to best suite the condition in network. 
                                                                [https://github.com/camaraproject/WorkingGroups/issues/29](https://github.com/camaraproject/WorkingGroups/issues/29)

                                                                **Status: Open / Discussed** 
                                                                \* QoD related topic are discussed 
                                                                 - Monitor API and Manage the "parameters" 
                                                                 - QoD members are encouraged to partcipate in the discussion
                                                                 
                                                                **-> Andrew will preapre material to be presented on the API Backlog** | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 17th of June | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17.md new file mode 100644 index 0000000000000000000000000000000000000000..9c0bb595b261e51603161eaba886e97c367ca8ba --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-06-17.md @@ -0,0 +1,52 @@ +# Camara QoD meeting + +### Date: 17 of June 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Ali Tizghdam (Telus)*** +* ***Jose Antonio Ordonez (TEF)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Joachim Dahlgren (E///)*** +* ***Ivan Nieto (Vodafone)*** +* ***Eric Muray (Vodafone)*** +* ***Tuan Tran (Broadpeak)*** +* ***Assane Niang (Orange)*** +* ***MBENGUE Assane Niang (INNOV/NET)*** +* ***Serena (SKT)*** +* ***Thorsten Lohmar*** +* ***Milan Lalovic (BT)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \- API version 1\.2\.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \- Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 12 [ Open: 3 , Closed: 9 ]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | - As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template

                                                                Status : Open/Active DEV *(Under-review /* **No-Change )** | +| Issue QoD#7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \- the operation is going to be performed through discovery
                                                                \- could be an additional way of addressing issue \#1 \(see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                                                                **Status : On-Hold (No-Change)** | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                                                                Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                                                                \* Priorities on validation, make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT solution developed with partners: AVP sample application presented
                                                                    [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                                                                *\* Following components discussed based on the AVP*
                                                                 *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                                                                   (SeNF - Service Enabling Network Function)
                                                                 - AVP Use case with Camara QoD description
                                                                   [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                                                                   **Update [3/6]:**
                                                                    M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)

                                                                \* Orange : conditions in which API is called
                                                                 -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **Goal : Service API will deliver consistent funcionality for End-users**
                                                                \* How to include into Transform Function 
                                                                \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                                                                **Transform Function**       
                                                                \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                                                                *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                                                                - On-going action proposed :    How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                                                                **UPDATE: Based on agreement during the community meeting [3/6], SeNF should contain Transform Function** | +| Issue#13 -  *Flow Description Mapping* | Ericsson | **Goal : Enhance QoD API with "Flow Description" already defined in 3GPP NEF**
                                                                \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                                                                \* Lose the flexibility to define multiple flows in an AS session. 
                                                                *\* Presented on the meeting and will improve based on community feedback*

                                                                **DECISION: Continue with User-Story and next vote via commnunity if include into the API release.** | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : 

                                                                Issue #29
                                                                *-* *API to Request the Status of the Network Traffic*   | | **Use Case: Adapting Video Encoding to the Network Conditions**
                                                                When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera.
                                                                The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 

                                                                **Status: Open/Discussed** **within API-Backlog**
                                                                **\- UPDATE: Use\-case proposal presented on the API Backlog meeting** | +| Issue #30
                                                                - *API to Route Traffic to a Specific Slice on the Network* | | **Use Case: Selectively Routing Traffic to a Network Slice**
                                                                An application has video traffic and configuration traffic. The application routes its Configuration Traffic over a slice
                                                                with higher quality of service and routes the video traffic over a slice with a lower quality of servi

                                                                **Status: Open/Dicussed within the API-backlog : might be related to QoD** | +| QoD Enhancement 
                                                                - *QoS Session reservation time extend* | Microsoft | **Goal: API enhancement to enable on-going QoS session renewal**
                                                                \* Currently QoD session can be specified with session duration \*Enhancement proposed : API for application extend/renew of on-going session (leasing a resource for a limited time and renewing the lease before it lapses until it is no longer needed) | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the 3rf of July
                                                                2\. Please contact topic owner \(@DT\) with any issues or requests | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01.md new file mode 100644 index 0000000000000000000000000000000000000000..4788291e3d64e2a3c73ae4fb9f53aca7f6f50024 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-01.md @@ -0,0 +1,46 @@ +# Camara QoD meeting + +### Date: 1st of July 2022 + +## Attendees + +* ***Marcin Jarząb (DT)*** +* ***Steffen Drüsedow(DT)*** +* ***Andrew Wajs (Scinera)*** +* ***Patrice Conil (Orange)*** +* ***Toshi WAKAYAMA (KDDI)*** +* ***Jan Friman (E///)*** +* ***Emil Zhang (E///)*** +* ***Eric Muray (Vodafone)*** +* ***Serena (SKT)*** +* ***Milan Lalovic (BT)*** + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| | | \* API version 1.2.0 specs are available at: [https://github.com/camaraproject/QualityOnDemand/tree/main/code/API\_definitions](https://github.com/camaraproject/QualityOnDemand/tree/main/code/API_definitions)
                                                                \* Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues \- thank you\! | +| **CURRENT ISSUES** | | **Total: 12 [ Open: 3 , Closed: 9 ]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | \* As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template

                                                                Status : Open/Active DEV *(Under-internal review)* | +| Issue QoD#7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities
                                                                \* the operation is going to be performed through discovery
                                                                \* could be an additional way of addressing issue #1 (see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1))

                                                                **Status : On-Hold (No-Change)** | +| Issue QoD#13
                                                                - *"Flow Description" Mapping* | Ericsson | Issue #13 : Enhance QoD API with "Flow Description" already defined in 3GPP NEF
                                                                \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                                                                \* Lose the flexibility to define multiple flows in an AS session. 
                                                                \* Proposal introduces API to define IP-Flows for single QoS session and assigned Profile
                                                                *\* Presented on the meeting and will improve based on community feedback*

                                                                **DECISION: Continue with User-Story and next community voting if include into the API release. UPDATE [1.07]: DT discussed proposal internaly, comments and communication on-going**  | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                                                                Orange | **GOAL: We need to start to summarize leassons learnt from Dev/Validate**   
                                                                \* Priorities on validation, make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT solution developed with partners: AVP sample application presented
                                                                    [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                                                                *\* **Following components discussed based on the AVP***
                                                                 *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                                                                   (SeNF - Service Enabling Network Function)
                                                                 - AVP Use case with Camara QoD description
                                                                   [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                                                                **Update [3.06]:** M.Jarzab & Morell will colaborate on further enhancements (UML , Call-flow / consider access technology 4G/5G NSA/SA)
                                                                \* Orange : conditions in which API is called
                                                                 -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **GOAL : Service API will deliver consistent funcionality for End-users**
                                                                \* How to include into Transform Function 
                                                                \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                                                                **Transform Function**       
                                                                \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                                                                *\- Focus on 3GPP & CAMARA\** API with Mappping Table presented (PPT will be distributed)
                                                                - On-going action proposed : How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                                                                **UPDATE [3.06]: Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **API Improvements / Updates** | | | +| QoD API Update 
                                                                *(error codes / description)* | DT | **QoD API - Please verify and update QoD def to v. 1.2.1 #14 :** [https://github.com/camaraproject/QualityOnDemand/pull/14](https://github.com/camaraproject/QualityOnDemand/pull/14)
                                                                \* No change in API functionality \* Error codes modified (improved description) and new added \* API description change  | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : *Issue* *#29*
                                                                *-* *API to Request the Status of the Network Traffic*   | Scenera | **Use Case: Adapting Video Encoding to the Network Conditions**
                                                                When processing data from a video camera the bandwidth required is highly dependent on the encoding settings within the camera. The bandwidth can be controlled by either changing the resolution of the video or the encoding quality. 

                                                                **Status: Open/Discussed** **within API-Backlog** 
                                                                Decision (TBC) : Still not decided where to assign | +| API Backlog : *Issue #30* 
                                                                - *API to Route Traffic to a Specific Slice on the Network* | Scenera | **Use Case: Selectively Routing Traffic to a Network Slice**
                                                                An application has video traffic and configuration traffic.
                                                                The application routes its Configuration Traffic over a slice with higher quality of service and routes the video traffic over a slice with a lower quality of service

                                                                **Status:** **CLOSED@API-Backlog** : [https://github.com/camaraproject/WorkingGroups/issues/30](https://github.com/camaraproject/WorkingGroups/issues/30)
                                                                Update [1.07] - Continue with Use case description to fit QoD requirements.  - Material presented / improvements requested (mobile connectivity / IP-Flows) | +| QoD Enhancement 
                                                                - *QoS Session reservation time extend* | Microsoft | **Goal: API enhancement to enable on-going QoS session renewal**
                                                                \* Currently QoD session can be specified with session duration \* Enhancement proposed : API for application extend/renew of on-going session (leasing a resource for a limited time and renewing the lease before it lapses until it is no longer needed)

                                                                **UPDATE (1.07) : Request for Microsoft confirmation**  - Ownership (proposal, user story etc.) and community final agreement (TBA) | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the July 15/2022
                                                                2\. Please contact topic owner \(marcin\.jarzab@external\.telekom\.de\) with requests/issues | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15.md new file mode 100644 index 0000000000000000000000000000000000000000..ebd2c79d64e4f395aa873e94c1fba21fb9431099 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-15.md @@ -0,0 +1,47 @@ +# Camara QoD meeting + +### Date: 15th of July 2022 + +## Attendees + +* Marcin Jarząb (DT) +* Steffen Drüsedow(DT) +* Toshi WAKAYAMA (KDDI) +* Petar Torre (Intel) +* Tuan Tran (Samsung) +* Milan Lalovic (BT) +* Mike Bowring (Spry fox networks) +* Ramesh Shanmugasundaram (Spry fox networks) +* Ivan Nieto (Vodafone) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through last MoM action items +* Identify additional tasks, prepare upcoming ones + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | +| ----------- | --- | --- | +| **Welcome & Recap** | | | +| | | Repository  address: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand) | +| **CURRENT STATUS** | | | +| *Overview* | | \* Currently contributed API definition needs to be updated for eg. to incorporate the versioning concept agreed within commonalities. Please see newly created issue [https://github.com/camaraproject/QualityOnDemand/issues/20](https://github.com/camaraproject/QualityOnDemand/issues/20)

                                                                \* Reviews from WG members discussed and worked on using open issues:
                                                                [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                \- topics started to be addressed within relevant GitHub issues | +| *Highlights* | | \* API documentation is contributed, waiting on review by the group (TBA)
                                                                \* API code will be contributed until end of July by DT and first complete version 0.x of the API will be on GitHub | +| **CURRENT ISSUES** | | **Total:14 [Open:3, Closed:11]** | +| Issue QoD#12
                                                                *\- Create user stories for QoD in line with Commonalities standard* | DT | \* As agreed previously in issue #3, please use the Commonalities User Story Template that has been just finalized 
                                                                  to align the QoD User Stories with the Camara common template.
                                                                \* Contribute user stories based on template.

                                                                Update (15.07) Status : Closed / In-review with following pull-requests 
                                                                \* User Story DOC - [https://github.com/camaraproject/QualityOnDemand/pull/19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                                                                \* Latency API - [https://github.com/camaraproject/QualityOnDemand/pull/18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                                                                \* BW API - [https://github.com/camaraproject/QualityOnDemand/pull/17](https://github.com/camaraproject/QualityOnDemand/pull/17) 

                                                                **Reviewer: *Support from Intel on reviewing the PR's.***

                                                                **Comment:**
                                                                -> Glossary DOC in commonalities (in-review) applicable to introduce&define common vocabulary (e.g. App-Flow/UL/DL) 
                                                                [https://github.com/camaraproject/WorkingGroups/pull/52](https://github.com/camaraproject/WorkingGroups/pull/52) | +| Issue QoD#7
                                                                *\- Add new endpoint in QoD API to request available qos\_profiles\(Discovery API\)* | DT | **Issue #7 (*enhancement*) labeled as QoD-backlog due to other on-going priorities**
                                                                \* the operation is going to be performed through discovery,
                                                                \* could be an additional way of addressing issue #1 (see Vodafone's [comment](https://github.com/camaraproject/QualityOnDemand/issues/1)).

                                                                **Status : On-Hold** | +| Issue QoD#13
                                                                - *"Flow Description" Mapping* | Ericsson | **Issue #13: Enhance QoD API with "Flow Description" already defined in 3GPP NEF**
                                                                \* Currently parametrisation approach is used (“ueAddr”, “uePorts”, ...) with flat data model difficult to evolve,
                                                                \* Lose the flexibility to define multiple flows in an AS session, 
                                                                \* Proposal introduces API to define IP-Flows for single QoS session and assigned Profile,
                                                                *\* Presented on the meeting and will improve based on community feedback.*
                                                                **UPDATE [15.07]: DT discussed proposal internaly and review provided.** | +| Issue QoD#20
                                                                *- Reset QoD API version* | DT | **Issue #20:** **Reset QoD API version**\* Versioning related guidelines agreed within commonalities working group, the QoD API version needs to be reset (e.g 0.x) | +| **NEW ISSUES / Discussion point** | | | +| Testing and Validation | DT,
                                                                Orange | **GOAL: We need to start to summarize lessons learnt from Dev/Validation**   
                                                                \* Priorities on validation, make some progress 
                                                                  -> test cases definition for BW/Latency management  
                                                                \* DT developed PoC with partners: AVP sample application presented
                                                                    [https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970](https://www.telekom.com/en/media/media-information/archive/automated-valet-parking-with-5g-648970)
                                                                *\* **Following components discussed based on the AVP***
                                                                 *\- Terminal \-\> *AF ->* CAMARA API (Exposure GW) -> SeNF\* -> NEF/SCEF interaction* 
                                                                   (SeNF - Service Enabling Network Function)
                                                                 - AVP Use case with Camara QoD description
                                                                   [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA\_AVP\_Short\_Overview.pptx](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/CAMARA_AVP_Short_Overview.pptx)
                                                                **Update [3.06]:**
                                                                \* M.Jarzab & Morell will colaborate on further enhancements (UML, Call-flow / considering access technology 4G/5G NSA/SA)
                                                                \* Orange : conditions in which API is called
                                                                 -  Activity on-going and what to expose will be discused and decided in Orange | +| Transform Function | TEF | **GOAL : Service API will deliver consistent funcionality for End-users**
                                                                \* How to include into Transform Function 
                                                                \* Testing workflow defined and included: CAMARA API / Transform / NEF 

                                                                **Transform Function**       
                                                                \* 3GPP VS CAMARA: AN OPENAPI COMPARISON presented by TEF 
                                                                 *\- Focus on 3GPP & CAMARA*
                                                                *\** API with Mappping Table presented (PPT will be distributed)
                                                                 - On-going action proposed: How to design for SeNF integration (Transfomers/Adapters) or being part of Exposure Gateway / API Management 
                                                                **UPDATE [3.06]: Based on agreement during the community meeting, SeNF should contain Transform Function** | +| **API Improvements / Updates** | | | +| QoD API Update 
                                                                *(error codes / description)* | DT | **QoD API - Please verify and update QoD def to v.1.2.1 #14 :** [https://github.com/camaraproject/QualityOnDemand/pull/14](https://github.com/camaraproject/QualityOnDemand/pull/14)
                                                                \* No change in API functionality, 
                                                                \* Error codes modified (improved description) and new added, 
                                                                \* API description change.  
                                                                 -> **UPDATE [15.07]** "Reverted" due to decision to change API versioning to 0.x since backward compatibility still not supported | +| **QoD **Proposals** & API Backlogs** | | | +| API Backlog : *Issue #30* 
                                                                - *API to Route Traffic to a Specific Slice on the Network* | Scenera | **Use Case: Selectively Routing Traffic to a Network Slice**
                                                                An application has video traffic and configuration traffic.
                                                                The application routes its Configuration Traffic over a slice with higher quality of service and routes the video traffic over a slice with a lower quality of service.

                                                                **Status:** **CLOSED@API-Backlog** : [https://github.com/camaraproject/WorkingGroups/issues/30](https://github.com/camaraproject/WorkingGroups/issues/30)
                                                                **Update [1.07]** \* Continue with Use case description to fit QoD requirements, 
                                                                \* Material presented / improvements requested (mobile connectivity / IP-Flows). | +| Enhancement :
                                                                 QoS Profiles Map | BT | \* Discuss idea from BT to enhance current QoS profiles mapping table to better fit actual mappings with Network Capabilities, 
                                                                \* Consider Transform Function as “component” which is responsible for those mappings, 
                                                                \* Update current QoD profiles (Low\_Latency, S\_Throughput, … -> High Priority Queue ), 
                                                                \* Issue will be created with details and proposed approach.  

                                                                [https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/BT\_Contributions\_CAMARA\_QoD.pdf](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/Contributions/BT_Contributions_CAMARA_QoD.pdf)
                                                                | +| **AOB** | | | +| | | 1\. Next QoD meeting in two weeks on the July 29/2022
                                                                2\. Please contact topic owner \(marcin\.jarzab@external\.telekom\.de\) with requests/issues | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29.md new file mode 100644 index 0000000000000000000000000000000000000000..e0dea137b3268291a04c340c0fa65486da966c18 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-07-29.md @@ -0,0 +1,47 @@ +# Camara QoD meeting + +### Date: 29th of July 2022 + +## Attendees + +* Toshi Wakayama (KDDI) +* Animesh Attri (Telus) +* Emil Zhang (Ericsson) +* Kevin (Vodafone) +* Kevin Zu (Verizon) +* José A. Ordóñez Lucena (Telefonica) +* Morel Sylvain (Orange) +* Mbengue Assan Niang (Orange) +* Tuan Tran (Broadpeak) +* Ramesh Shanmugasundaram (Spry fox networks) +* Herbert Damker (DT) +* Anja Gerlach (DT) +* Shilpa Padgaonkar (DT) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | | +| Issues and Pull Requests | |
                                                                • Issues:19 [Open:8, Closed:11]
                                                                • Pull requests:11 [Open:7, Closed: 4]
                                                                | | +| **HIGHLIGHTS** | |
                                                                • QoD service implementation contributed to Camara
                                                                • QoD API version reset done to 0.1.0 
                                                                | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                Status: Ongoing | Ericsson |
                                                                • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                                                                • Herbert will create the new issues as agreed
                                                                | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                                                                *Status: New* | DT |
                                                                • API version has been reset to 0.1.0. 
                                                                • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                                                                • Agreed reviewers
                                                                  • Jose
                                                                • Request additional members to nominate themselves as reviewers 
                                                                | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution 
                                                                *Status: New* | DT |
                                                                • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                                                                • No reviweres selected in today's meeting
                                                                • Details of the contribution are available here 
                                                                • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD)
                                                                  [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                                                                | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                                                                *Status: New* | DT |
                                                                • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                                                                • New topics from Sylvain and Jose:
                                                                  • How to ensure completeness of security review? Issue to be opened in commanalities by Shilpa
                                                                  • In what format should test cases be contributed? Issue to be opened in Commonalities by Shilpa
                                                                  • Can DT provide some sample test data for QoD tests? DT will check internally and get back on this topic
                                                                | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                                                                Status: Ongoing | DT
                                                                Intel
                                                                Vodafone | Following pull requests are currently in review
                                                                • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                                                                • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                                                                • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                                                                Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                Status: New | |
                                                                • Will be fixed with a PR
                                                                | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                                                                Status: New | Verizon |
                                                                • Points 1,2,3 are either covered as a part of ongoing Documentation reviews or are a duplicate of [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                • Point4 is already in the internal backlog of DT for one of the upcoming releases.
                                                                  Shilpa will create an issue in QoD to address this point..
                                                                | | +|
                                                                **NEW ISSUES / Discussion point** | | | | +| | |
                                                                • Herbert: Is approval from 2 reviewers enough to merge a PR?
                                                                • Shilpa: How long should an inactive review stay open?
                                                                • Jose: The current implementation does not include in scope the consent mangement aspect. Shilpa will restart this discussion in Commanalities as it has impact on several other API families.
                                                                | | +| **AOB** | | | | +| | | Next QoD meeting in two weeks on the Aug 12/2022 | | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12.md new file mode 100644 index 0000000000000000000000000000000000000000..9b491a07f48f37e3bf6b993527a4407c00b4231b --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-08-12.md @@ -0,0 +1,52 @@ +# Camara QoD meeting + +### Date: 12th August 2022 + +## Attendees + +* Toshi Wakayama (KDDI) +* Emil Zhang (Ericsson) +* Jan Friman (Ericsson) +* Eric Murray (Vodafone) +* Andrew Wajs (Scinera) +* Syed R (Verizon) +* Patrice Conil (Orange) +* Animesh Attri (Telus) +* Shilpa Padgaonkar (DT) + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | | +| Issues and Pull Requests | |
                                                                • Issues:26[Open:14, Closed:12]
                                                                • Pull requests:12 [Open:8, Closed: 4]
                                                                | | +| **HIGHLIGHTS** | |
                                                                • Patrice would like to contribute a second reference implementation for QoD. To be checked with Markus Kümmerle where we can place this
                                                                | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                Status: Ongoing | Ericsson |
                                                                • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                                                                • Shilpa will create the new issues as agreed
                                                                • This later comments will be reviewed by Eric to see if this issue can be closed.
                                                                | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                                                                *Status: New* | DT |
                                                                • API version has been reset to 0.1.0. 
                                                                • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                                                                • Agreed reviewers
                                                                  • Jose and Emil
                                                                | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution 
                                                                *Status: New* | DT |
                                                                • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                                                                • No reviweres selected in today's meeting
                                                                • Details of the contribution are available here 
                                                                • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD) [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                                                                | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                                                                *Status: New* | DT |
                                                                • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                                                                • No reviewers yet
                                                                | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                                                                Status: Ongoing | DT
                                                                Intel
                                                                Vodafone | Following pull requests are currently in review
                                                                • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                                                                • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                                                                • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                                                                Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                Status: Ongoing | |
                                                                • Will be fixed with a PR
                                                                | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                                                                Status:Ongoing | Verizon |
                                                                • This issue wil be closed as points moved to [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request 
                                                                Status: New | Orange | Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                                                                Status: New | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                Status: New | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                                                                Status: New | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38)  after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                Status: New | Verizon | DT will address this in a later PR | | +|
                                                                **NEW ISSUES / Discussion point** | | | | +| | |
                                                                • Should a company that has agreed to implement a CAMARA API, be assigned as automatic reviewer for the API contribution?
                                                                • Where do we track which company has agreed to implement a certain Camara API?
                                                                • Describe process to approve a PR
                                                                • What should be done if no reviewers available for certain PRs?
                                                                • Above points will be raiesd in next Steerco
                                                                | | +| **AOB** | | | | +| | | Next QoD meeting in two weeks on the Aug 26 2022 | | +
                                                                +# MOM-2022-08-12 + +Fri, Aug 12, 2022 10:52 PM diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09.md new file mode 100644 index 0000000000000000000000000000000000000000..7a4f7092808ee60fc76ed27dd8b07ac4fb558eb7 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-09.md @@ -0,0 +1,45 @@ +# Camara QoD meeting + +### Date: 09th September 2022 + +## Attendees + +* Emil Zhang (Ericsson) +* José A. Ordóñez Lucena (Telefonica) +* Eric Murray (Vodafone) +* Patrice Conil (Orange) +* ... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | | +| Issues and Pull Requests | |
                                                                • Issues:27[Open:15, Closed:12]
                                                                • Pull requests:12 [Open:8, Closed: 4]
                                                                | | +| **HIGHLIGHTS** | |
                                                                • Patrice would like to contribute a second reference implementation for QoD. To be checked with Markus Kümmerle where we can place this
                                                                | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                Status: Ongoing | Ericsson |
                                                                • Emil agrees to split the issues into smaller dedicated issues as proposed by DT
                                                                • Shilpa will create the new issues as agreed
                                                                • This later comments will be reviewed by Eric to see if this issue can be closed.
                                                                | | +| [#32](https://github.com/camaraproject/QualityOnDemand/issues/32) Resolving “protocolIn”/“protocolOut” with a better parameter design
                                                                Status: Ongoing | Ericsson |
                                                                • Ericsson suggests changing 'UPLINK'/'DOWNLINK' to 'FROM_UE'/'TO-UE' in 'Direction' enum. The community is happy with it. 
                                                                • Pull request [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is ready to merge. 
                                                                | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                                                                Status: Ongoing | DT |
                                                                • API version has been reset to 0.1.0. 
                                                                • Request to review pull requests [PR24](https://github.com/camaraproject/QualityOnDemand/pull/24) [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                                                                • Agreed reviewers
                                                                  • Jose and Emil
                                                                  • Emil has approved the PRs
                                                                | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution
                                                                Status: Ongoing | DT |
                                                                • Request to review [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28) 
                                                                • No reviweres still
                                                                • Details of the contribution are available here 
                                                                • [https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code/README.MD](https://github.com/camaraproject/QualityOnDemand/blob/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code/README.MD) [https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API\_code](https://github.com/camaraproject/QualityOnDemand/tree/44621c440abf4e89107ebd48a4465d171bdff16c/code/API_code)
                                                                | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                                                                Status: Ongoing | DT |
                                                                • Request to review [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                                                                • No reviewers yet
                                                                | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                                                                Status: Ongoing | DT
                                                                Intel
                                                                Vodafone | Following pull requests are currently in review
                                                                • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                                                                • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                                                                • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                                                                Request Kevin and Petar to resolve comments which have been worked on and where applicable. | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                Status: Ongoing | |
                                                                • Will be fixed with a PR
                                                                | | +| [#22](https://github.com/camaraproject/QualityOnDemand/issues/22) Clarification needed
                                                                Status: Ongoing | Verizon |
                                                                • This issue wil be closed as points moved to [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request
                                                                Status: Ongoing | Orange |
                                                                • Ericsson is willing to propose a solution too
                                                                | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                                                                Status: Ongoing | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                Status: Ongoing | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                                                                Status: Ongoing | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                Status: Ongoing | Verizon | DT will address this in a later PR | | +|
                                                                **NEW ISSUES / Discussion point** | | | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39)
                                                                Status: New* | Telefonica | Telefonica will address this in a later PR | | +
                                                                +# MOM-2022-09-09 diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23.md new file mode 100644 index 0000000000000000000000000000000000000000..14c1b16ae48d5b4fe1525d3213ddb1d8927bb021 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-09-23.md @@ -0,0 +1,61 @@ +# Camara QoD meeting + +### Date: 23rd September 2022 + +## Attendees + +* Emil Zhang (Ericsson) +* José A. Ordóñez Lucena (Telefonica) +* Eric Murray (Vodafone) +* Patrice Conil (Orange) +* Herbert Damker (Deutsche Telekom) +* Shilpa Padgaonkar (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Kevin Smith (Vodafone) +* Mahesh Chapalamadugu (Verizon) +* Mike Bowring (Spry Fox Networks) +* Sylvain Morel (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Ravi Kamalendiran (Axiata) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | | +| Issues and Pull Requests | |
                                                                • Issues: 29 [Open:17, Closed:12]
                                                                • Pull requests: 14 [Open:9, Closed: 5]
                                                                | | +| **HIGHLIGHTS** | |
                                                                • DT has created a new issue and provided a pull request for v0.8.0 of QOD API, which includes changes proposed from and discussed with several parties. The proposal combines the previous two QoD APIs into one.
                                                                | | +| **OPEN PULL REQUESTS** | | | | +| [#17](https://github.com/camaraproject/QualityOnDemand/pull/17)[#18](https://github.com/camaraproject/QualityOnDemand/pull/18) [#19](https://github.com/camaraproject/QualityOnDemand/pull/19) [#24](https://github.com/camaraproject/QualityOnDemand/pull/24) [#25](https://github.com/camaraproject/QualityOnDemand/pull/25) [#28](https://github.com/camaraproject/QualityOnDemand/pull/28) [#30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                                                                Status: In review | |
                                                                • Agreement to merge all artefacts related to v0.1.0 of the QoD APIs "low-latency" and "throughput" to preserve the material as reference and base within the repository history (User Story, API documentation, reference implementation code).
                                                                • The work will be continued on the combined single QoD API as proposed in v0.8.0, artefacts need to be updated as soon as possible.
                                                                | | +| [#37](https://github.com/camaraproject/QualityOnDemand/pull/37)
                                                                Status: In review | Ericsson |
                                                                • The proposed changes to v0.1.0 of stable-latency API will be superseeded by v0.8.0 (deleting the stable-latency API)
                                                                • The addressed issue of ambiguity of protocolIn/protocolOut parameters will not exist in v0.8.0 as these parameters are obmitted in the v0.8.0 version
                                                                • The pull request will be closed. The proposal of a flowinfo structure should be preserved as feature request in the backlog. Herbert will create an issue for that.
                                                                | | +| [#43](https://github.com/camaraproject/QualityOnDemand/pull/43)
                                                                Status: new pull request | |
                                                                • Akos presented the pull request and the related issue [#42](https://github.com/camaraproject/QualityOnDemand/issues/42)
                                                                • The main point is the combination of previous seperated APIs for stable latency and throughput into one combined API
                                                                • The existing comments were discussed. Mahesh created issues for his comments which will be addressed after implementation of v0.8.0
                                                                • Participants need more time for reviews, PR will kept open until next call on Oct 7
                                                                • DT will update the reference implementation based on proposed v0.8.0 of the API
                                                                | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13)
                                                                Status: Ongoing | Ericsson |
                                                                • Introduction of a flowinfo structure should get a feature request within backlog, see discussion of PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37) above
                                                                • UE ID aspect is addressed within v0.8.0 with UeId structure
                                                                | | +| [#32](https://github.com/camaraproject/QualityOnDemand/issues/32) Resolving “protocolIn”/“protocolOut” with a better parameter design
                                                                Status: Ongoing | Ericsson |
                                                                • Ambiguity of protocolIn/protocolOut parameters is "resolved" in v0.8.0, by deleting the parameters
                                                                • The proposal of PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37) should be preserved for backlog
                                                                | | +| [#20](https://github.com/camaraproject/QualityOnDemand/issues/20) API version reset
                                                                Status: Ongoing | DT |
                                                                • Will be closed with merge of [PR25](https://github.com/camaraproject/QualityOnDemand/pull/25)
                                                                | | +| [#26](https://github.com/camaraproject/QualityOnDemand/issues/26) QoD Code Contribution
                                                                Status: Ongoing | DT |
                                                                • Will be closed by merge of [PR28](https://github.com/camaraproject/QualityOnDemand/pull/28), see above
                                                                | | +| [#29](https://github.com/camaraproject/QualityOnDemand/issues/29) QoD API minimum readiness doc
                                                                Status: Ongoing | DT |
                                                                • Will be closed by merge of [PR30](https://github.com/camaraproject/QualityOnDemand/pull/30)
                                                                | | +| [#27](https://github.com/camaraproject/QualityOnDemand/issues/27) QoD API documentation
                                                                Status: Ongoing | DT |
                                                                • Will be closed by merge of
                                                                  • [PR17](https://github.com/camaraproject/QualityOnDemand/pull/17)
                                                                  • [PR18](https://github.com/camaraproject/QualityOnDemand/pull/18)
                                                                  • [PR19](https://github.com/camaraproject/QualityOnDemand/pull/19)
                                                                • Documentation need to be updated to reflect changes of v0.8.0
                                                                | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39)
                                                                Status: Ongoing | Telefonica | Will be closed when PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) is merged | | +| **Remaining issues not discussed due to lack of time** | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                Status: Ongoing | |
                                                                • Will be fixed with a PR
                                                                | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request
                                                                Status: Ongoing | Orange |
                                                                • Ericsson is willing to propose a solution too
                                                                | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                                                                Status: Ongoing | Vodafone | This can be closed once [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is merged | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                Status: Ongoing | Vodafone | Awaiting feedback from members | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                                                                Status: Ongoing | Orange | Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                Status: Ongoing | Verizon | DT will address this in a later PR | | +
                                                                diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07.md new file mode 100644 index 0000000000000000000000000000000000000000..beb68f55cbfe7a2ae4bb21e911601b0279242f51 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-07.md @@ -0,0 +1,57 @@ +# Camara QoD meeting + +### Date: 7th October 2022 + +## Attendees + +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Mahesh Chapalamadugu (Verizon) +* Mike Bowring (Spry Fox Networks) +* Milan Lalovic (BT) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Ravi Kamalendiran (Axiata) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* .... + +QoD minutes : [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +Goals + +* Go through existing action items +* Extend the action item list with new topics/issues/proposals + +## Agenda Proposal / Discussion items + +| Agenda Item | Who | | | +| ----------- | --- | --- | --- | +| **CURRENT STATUS** | | | | +| Overview | |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | | +| Issues and Pull Requests | |
                                                                • Issues: 36 [Open:18, Closed:18]
                                                                • Pull requests: 16 [Open: 1, Closed: 15]
                                                                | | +| **HIGHLIGHTS** | |
                                                                • Artefacts for v0.1.0 merged into main as agreed within last call, related issues closed
                                                                • PR #37 closed (not merged), as agreed. New issue #51 created
                                                                • Some clean-up done withing the repository, see PR 
                                                                | | +| **OPEN PULL REQUESTS** | | | | +| [#48](https://github.com/camaraproject/QualityOnDemand/pull/48) Update MAINTAINERS.MD | KDDI |
                                                                • Add Toshi Wakayama to sub projects maintainers
                                                                • Supported and no objections; merged
                                                                | | +| [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) Contribution of the QoD-API spec v0.8.0 | DT |
                                                                • Pull request was presented in last call, 14 days for feedback were agreed
                                                                • Joachim noted that Ericsson has started an internal review, but not able to enter the feedback yet due to vacations. Emil will enter the review during next week.
                                                                • If possible only urgent fixes should be done within the review, other points should be addressed as issues to be worked on after the combined API v0.8.0 is the new common base.
                                                                • Discussion about [code/API\_definitions/QoSProfile\_Mapping\_Table.md](https://github.com/camaraproject/QualityOnDemand/pull/43/files#diff-d944f3af37e3d99156930a944badae74c04f6fc2c2937657ed60ece9df752b00 "code/API_definitions/QoSProfile_Mapping_Table.md")
                                                                  • The content of the table has not changed, just the names of the profile where replaced
                                                                  • The note should emphasize that it is just an example how the QoS Profiles can be mapped and not binding for operators.
                                                                  • There is a notion that guranteed bit rate (GBR) can be offered only in limited scenarios (e.g. campus). The table is currently providing only examples for relative prioritization.
                                                                  • Proposals for changed wording (e.g. "up to xx Mbit" replaced with more use case oriented wording) are welcome.
                                                                | | +| **OPEN ISSUES** | | | | +| [#13](https://github.com/camaraproject/QualityOnDemand/issues/13) "Flow Description" Mapping
                                                                Status: Superseded by #51 | Ericsson |
                                                                • Created new issue based on (closed) PR [#37](https://github.com/camaraproject/QualityOnDemand/pull/37):
                                                                  • [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                                                                  • Herbert will ask Emil to close #13 as superseded.
                                                                  • UE ID aspect is addressed within v0.8.0 with UeId structure
                                                                | | +| [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) #23 Consistent use of the term notification URL in API docs
                                                                Status: Ongoibg | |
                                                                • Will be fixed with a later PR
                                                                | | +| [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                Status: Ongoing | Verizon |
                                                                • DT will address this in a later PR
                                                                | | +| [#33](https://github.com/camaraproject/QualityOnDemand/issues/33) Small API modification to reduce consumption
                                                                Status: Ongoing | Orange |
                                                                • Added feature request [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) after discussions to address the issue
                                                                | | +| [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                Status: Ongoing | Vodafone |
                                                                • Awaiting feedback from members
                                                                | | +| [#36](https://github.com/camaraproject/QualityOnDemand/issues/36) Asymmetric QoS Flows
                                                                Status:Superseded by #51? | Vodafone |
                                                                • As [PR37](https://github.com/camaraproject/QualityOnDemand/pull/37) is not merged there is now new issue #51
                                                                | | +| [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                                                                Status: Ongoing | Orange |
                                                                • Ericsson is willing to propose a solution too
                                                                | | +| [#39](https://github.com/camaraproject/QualityOnDemand/issues/39) Typo in SessionInfo definition.
                                                                Status: PR in review | Telefonica |
                                                                • Will be closed when PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) is merged
                                                                | | +| [#40](https://github.com/camaraproject/QualityOnDemand/issues/40) Definition of flowid in NEF API AfSessionWithQosSubscription
                                                                Status: Discussion | Spry Fox Networks |
                                                                • See comment from Eric
                                                                | | +| [#42](https://github.com/camaraproject/QualityOnDemand/issues/42) QoD API specification version 0.8.0
                                                                Status: PR in review | DT |
                                                                • See PR [#43](https://github.com/camaraproject/QualityOnDemand/pull/43) above
                                                                | | +| **NEW ISSUES** | | | | +| [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                                                                Status: new | Verizon |
                                                                • as discussed 2022-09-23
                                                                | | +| [#45](https://github.com/camaraproject/QualityOnDemand/issues/45) Need to support ability to configure fallback qos
                                                                Status: new | Verizon |
                                                                • as discussed 2022-09-23
                                                                | | +| [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                                                                Status: new | Verizon |
                                                                • as discussed 2022-09-23
                                                                | | +| [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                                                                Status: new | Verizon |
                                                                • as discussed 2022-09-23
                                                                | | +| [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                                                                Status: new | Ericsson |
                                                                • as discussed 2022-09-23, to preserve closed PR #37, superseding #13 (?) and #36 (?)
                                                                | | +| | | | | +| [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx
                                                                Status: new | | | | \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21.md new file mode 100644 index 0000000000000000000000000000000000000000..0c9eef979b3b1609bca2198819ac09ecdc2368c7 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-10-21.md @@ -0,0 +1,68 @@ +# Camara QoD meeting + +*21st October 2022* + +## Attendees + +* Andrew +* Assane Mbengue (Orange) +* Eric Murray (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Rocio Otiz Peña () +* Syed A Rehman (Verizon) +* Sylvain Morel (Orange) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Rec +* Housekeeping +* v0.8.0 merged - next steps +* Development branch for v0.9.0? +* Open issues and pull requests +* New issues +* Any other issues + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap & Recent Updates** | | +| |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | +| **Housekeeping** | | +| | Mailinglist: Please subscribe to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-qod](https://lists.camaraproject.org/g/sp-qod)
                                                                The list will be used for invitations and discussions between members of the sub project. The address is: sp-qod@lists.camaraproject.org | +| | Team call: need to replace the current Teams link (Herbert). Will be distributed via mailing list and within the README.md +| **API Definition v0.8.0 merged** | | +| | [QoD API Spec v0.8.0](https://github.com/camaraproject/QualityOnDemand/blob/main/code/API_definitions/qod-api.yaml) merged. See [#42](https://github.com/camaraproject/QualityOnDemand/issues/42) for a summary of changes.
                                                                Documentation and reference implementation to be updated -> new issues. | +| | (Server) Reference implementations should go into seperate repositories , allowing multiple reference implementation without conflicts. Waiting for issue [#63](https://github.com/camaraproject/WorkingGroups/issues/63) in Commonatilities to be resolved. | +| **Branch for development of v0.9.0** | | +| | Main branch to be protected (no direct push, at least one review, codeowner review will automatically requested). For development of next iteration of the the API definition we create a branch to bundle multiple of the issues before updating main (done, new branch: [dev-v0.9.0](https://github.com/camaraproject/QualityOnDemand/tree/dev-v0.9.0)) | +| **Open Issues** | | +| | [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions
                                                                Ericsson volunteered to work on a PR. | +| | [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                                                                Ongoing discussion | +| | [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                                                                Syed will add more information +| | [#45](https://github.com/camaraproject/QualityOnDemand/issues/45) Need to support ability to configure fallback qos
                                                                Backlog: Alternative QoS class will require a discovery function of available QoS profiles first, see #7. Until then clear documentation what happens if requested QoS profile can not be provided by the network -> new issue | +| | [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                                                                Important enhancement; dependency on Commonality workgroup +| | [#41](https://github.com/camaraproject/QualityOnDemand/issues/41) Impact on Camara on the definition of flowid in NEF API AfSessionWithQosSubscription
                                                                Ongoing discussion; Request to add information about concrete impact on Camara QoD API | +| | [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                                                                Ongoing; Ericsson is willing to propose a solution | +| | [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                Request to provide a PR for the solution proposed (two optional parameters: private and public IPv4Addr) | +| | [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                DT will address this in a later PR | +| | [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                Will be fixed with a later PR | +| | [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) Add new endpoint in QoD API to request available qos_profiles
                                                                Backlog item | +| **NEW ISSUES** | | +| | [#56](https://github.com/camaraproject/QualityOnDemand/issues/56) Protect main branch and create branch for development of version v0.9.0
                                                                Rule added to repo configuration; PR [Update CODEOWNERS #55](https://github.com/camaraproject/QualityOnDemand/pull/55) created; Branch [dev-v0.9.0](https://github.com/camaraproject/QualityOnDemand/tree/dev-v0.9.0) created| +| | [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) Update of User Story | +| | [#58](https://github.com/camaraproject/QualityOnDemand/issues/58) Update of API documentation | +| | [#59](https://github.com/camaraproject/QualityOnDemand/issues/59) Document what happens if requested QoS profile can not be provided | +| | [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx | +| **Any other issue** | | +| | Next QoD community call on Nov 4th diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04.md new file mode 100644 index 0000000000000000000000000000000000000000..ccbbe03d9943c5f3e5d722edaa0dddcd45a79513 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-11-04.md @@ -0,0 +1,73 @@ +# Camara QoD meeting + +*21st October 2022* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Diego Marí Moretón (Meta) +* Eric Murray (Vodafone) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jane Shen (Mavenir) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Maria Virtudes Briz Ruiz (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Syed A Rehman (Verizon) +* Sylvain Morel (Orange) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Housekeeping +* Update maintainers.md +* Pull Request #62 - Improvement proposal for QoSProfile_Mapping_Table.md +* Update on issues +* Any other issues + +## Discussion + +| Agenda Item | Description | +| ----------- | ------------| +| **Recap & Recent Updates** | | +| |
                                                                • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                | +| **Housekeeping** | | +| | Mailinglist: Please subscribe if not yet done to the mailinglist of the subproject here: [https://lists.camaraproject.org/g/sp-qod](https://lists.camaraproject.org/g/sp-qod)
                                                                The list will be used for invitations and discussions between members of the sub project. The address is: sp-qod@lists.camaraproject.org | +| | Team call: new Teams meeting link distributed within invitation and within README.md. Time changed to UTC 13:00, due to change to wintertime in EU +| | Main branch is now protected, a merge requires at least one review by a codeowner. Codeowner will take care to involve current maintainers and invovled contributors in relevant pull request reviews. +| | Branch dev-v0.9.0 created for changes which are targeted for the next version of the API definition. Use this branch as target for change requests of the current API yaml file. +| **Update of MAINTAINERS.MD** | | +| | Jose A Ordonez Lucena resigned as maintainer and proposed Jose Luis Urien with Jesus Peña as standin as new maintainers within the subproject. Accepted without objections, change to MAINTAINERS.MD merged | +| **PR #62 - Improvement proposal for QoSProfile_Mapping_Table.md** | | +| | Thorsten presented his pull request to improve the QoSProfile_Mapping_Table with the aim to make it more understandable for developers. Comments were discussed, the PR should be continued with updates based on the discussion.
                                                                • The example character has to be emphasized, it is too early to agree already on numers
                                                                • Eric's comment can be partly addressed partly by using "statistically assured" instead of "assured" (to make clear that it isn't contractually assured)
                                                                • Going forward a realization of issue #7 (Add new endpoint in QoD API to request available qos_profiles) should support QoS profile definitions together with KPIs | +| **Open Issues (without backlog)** | | +| | [#61](https://github.com/camaraproject/QualityOnDemand/issues/61) QoSProfile_Mapping_Table.md should be improved:
                                                                • new issue, will be fixed by PR #62 discussed above. +| | [#59](https://github.com/camaraproject/QualityOnDemand/issues/59) Document what happens if requested QoS profile can not be provided
                                                                • to addressed within #58 | +| | [#58](https://github.com/camaraproject/QualityOnDemand/issues/58) Update of API documentation
                                                                • Assigned to Deutsche Telekom, will provide PR | +| | [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) Update of User Story
                                                                • No update | +| | [#56](https://github.com/camaraproject/QualityOnDemand/issues/56) Protect main branch and create branch for development of version v0.9.0:
                                                                • closed, see housekeeping above. +| | [#52](https://github.com/camaraproject/QualityOnDemand/issues/56) Solution for multiple reference implementations for QualityOnDemand:
                                                                • Commonality working group came to decision to move API (provider) implementations outside the subproject repository. Which means DT and Orange will have separate repositories for managing their individual QoD solutions in Camara. Details to be defined. +| | [#51](https://github.com/camaraproject/QualityOnDemand/issues/51) Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions:
                                                                • Ericsson will work on PR, but current priority on #38. | +| | [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) need to include support for /PUT sessions
                                                                • No update; ongoing discussion | +| | [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) GET /sessions is missing status information
                                                                • No update; Syed will add more information +| | [#44](https://github.com/camaraproject/QualityOnDemand/issues/44) Parameter names used in the API spec need to be revisited to make them more developer friendly
                                                                • No update; Important enhancement; dependency on Commonality workgroup +| | [#41](https://github.com/camaraproject/QualityOnDemand/issues/41) Impact on Camara on the definition of flowid in NEF API AfSessionWithQosSubscription
                                                                • Mike added further explanation, community requested to discuss if this issue impacts Camara QoD directly. 3GPP members to consider to take it into 3GPP. | +| | [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) Feature request Add SUCCESSFUL\_RESOURCES\_ALLOCATION to QosChanged
                                                                • Ongoing; Ericsson is working on a solution proposal | +| | [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) Resolving ueAddr ambiguity when it is the UE private address
                                                                • Solution proposal from Eric is supported; he will work on a PR | +| | [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) Handle callbacks securely
                                                                • No update: DT will address this in a later PR | +| | [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) Consistent use of the term notification URL in API docs
                                                                • No update; Need to be fixed with a later PR | +| **New Issues** | | +| | [#nn](https://github.com/camaraproject/QualityOnDemand/issues/nn) xxx | +| **Any other issue** | | +| | Next QoD community call on Nov 18th, UTC 13:00, CET 14:00 diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02.md b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02.md new file mode 100644 index 0000000000000000000000000000000000000000..c857e410abe26930845fde36fd59eb9344663447 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2022/MOM-2022-12-02.md @@ -0,0 +1,50 @@ +# Camara QoD meeting + +*December 2nd, 2022* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Diego Marí Moretón (Meta) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* .... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Recap & Recent Updates +* Open Pull Requests (3) +* New Issues +* Next calls + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| **Recap & Recent Updates** | | +| |
                                                                  • Repo: [https://github.com/camaraproject/QualityOnDemand](https://github.com/camaraproject/QualityOnDemand)
                                                                  • Issues: [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) 
                                                                  • Pull Requests: [https://github.com/camaraproject/QualityOnDemand/pulls](https://github.com/camaraproject/QualityOnDemand/pulls)
                                                                  | +| **PR #71 - Update qod api documentation to 0.8.0** | | +| |
                                                                  • Thanks to Thorsten for his detailed review of the documentation. Most comments/suggestions are committed, result is fine for Thorsten
                                                                  • Some comments need to be addressed in API definition & documentation (=> issue for v0.9.0)
                                                                  • Agreement to commit the current version as soon as possible to have a base for further improvements. Jose Luis Urien will do a final review (Update: done & minor suggestion committed).
                                                                  • After merge of the current PR Herbert will initiate a minor editorial PR, mainly to split up the current huge line 99 to ease later reviews
                                                                  • Afterwards furhter fixes can be proposed
                                                                  | +| **PR #73 - Reduce to one example QoSProfile\_Mapping\_Table.md** | | +| |
                                                                  • No objection to the proposal in issue #72 and PR #73
                                                                  • Jose Luis Urien will do a final review from TEF perspective (Update: Suggestion to be more aligned with short term implementions done & committed)
                                                                  | +| **PR #67 - Introduce 'qosStatus' and corresponding notification event to fix issue #38** | | +| |
                                                                  • The presentation done in last call by Emil was helpful for the understanding of the PR
                                                                  • Emil updated the PR according to the comments
                                                                  • Reviews by TEF (Jose Luis Urien), KDDI (Toshi) and DT (as codeowner) to be done
                                                                  | +| New Issues | | +| |
                                                                  • Commonalities has agreed on API guidelines. Jose Luis Urien will create an issue and PR for version 0.9.0
                                                                  | +| **Next Calls** | | +| |
                                                                  • Next QoD community call on Friday, Dec 16th, UTC 13:00, CET 14:00
                                                                  • Call on Dec 16th will be skipped
                                                                  • First call in 2023 on Friday, January 13th, UTC 13:00, CET 14:00
                                                                  | diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13.md new file mode 100644 index 0000000000000000000000000000000000000000..ab1fb3615051d26984be466d0e3fd4a57897cbd1 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-13.md @@ -0,0 +1,56 @@ +# Camara QoD meeting - MOM-2023-01-13 + +*Januar 13th, 2023* + +## Attendees + +* Andrew +* Babu Narayan (?)(Nabstract) +* Diego Marí Moretón (Meta) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Joachim Dahlgren (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* Vaibhav Mehta (Nabstract) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Release planning +* Issues to "fix" 0.8.0 +* Review of open issues and PRs (esp. [#67](https://github.com/camaraproject/QualityOnDemand/pull/67), [#34](https://github.com/camaraproject/QualityOnDemand/issues/34), [#52](https://github.com/camaraproject/QualityOnDemand/issues/52)) +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| Release Planning | We need a release and branching strategy for our sub projects:
                                                                  • Releases to be done with Github release feature
                                                                  • Current status of main to be "released" as v0.8.0
                                                                  • As long as we are in v0.x.x backward compatibility is not mandatory, current status is "alpha"
                                                                  • Issues and PRs with small (bug) fixes (see next agenda item) to be addressed short-term and to be released as v0.8.1
                                                                  • Issues and PRs with larger changes (e.g. #67, #34) will go into v0.9.0 ("alpha2" release)
                                                                  See also issue [#118](https://github.com/camaraproject/WorkingGroups/issues/118) in Commonalities and the related PR with draft for versioning guidelines. | +| Issues for "fix" release v0.8.1 | Several issues and PR are addressing smaller typos, bugs, missing error codes etc:
                                                                  • PR [#77](https://github.com/camaraproject/QualityOnDemand/pull/77) \- Fixed couple of typos =\> to be merged \(UPDATE: done\)
                                                                  • Issue #83 - Internal server error 500 missing for GET & DELETE procedures=> addressed with PR [#86](https://github.com/camaraproject/QualityOnDemand/pull/86) (UPDATE: merged after review)
                                                                  • Issue [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) \- Consistent usage of notificationUri vs notificationUrl=\> will be addressed by DT \(UPDATE: done with new issue [#88](https://github.com/camaraproject/QualityOnDemand/issues/88) and PR [#89](https://github.com/camaraproject/QualityOnDemand/pull/89))
                                                                  • Issue [#84](https://github.com/camaraproject/QualityOnDemand/issues/84) \- \[qod\-api\.yaml\]: IPv6\-object will be generated instead of a String=\> to be discussed if this is a short\-term fix\, probably not
                                                                  • Issue [#81](https://github.com/camaraproject/QualityOnDemand/issues/81) \- Introducing error code 501 "Not Implemented"=\> DT will provide PR
                                                                  • Potential further minor fixes, e.g. in documentation
                                                                  | +| PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67) |
                                                                  • Open conversations from review discussed => can be marked as resolved (Emil)
                                                                  • PR need to be rebased against main branch after fix release v0.8.1 is done
                                                                  • Documentation need to be updated according to the changes (within PR or in separate one?)
                                                                  | +| Issue [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) |
                                                                  • PR will be provided by Eric after PR #67 is done
                                                                  | +| Issue [#52](https://github.com/camaraproject/QualityOnDemand/issues/52) |
                                                                  • Two new repos created for provider implementation (PI)
                                                                  • [QualityOnDemand_PI1](https://github.com/camaraproject/QualityOnDemand_PI1) for DT’s provider implementation
                                                                  • [QualityOnDemand_PI2](https://github.com/camaraproject/QualityOnDemand_PI2) for Orange’s provider implementation
                                                                  | + +## PRs that can be merged + +* PRs for fixes as listed above after being reviewed + +## Issues that can be closed + +* Issue [#52](https://github.com/camaraproject/QualityOnDemand/issues/52) can be closed, repos for provider implementations created + +## AOB + +\* Next call is on January 27th. \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27.md new file mode 100644 index 0000000000000000000000000000000000000000..94cfd03f45b7fa98e9151b437bf9f1ae0eba29c0 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-01-27.md @@ -0,0 +1,70 @@ +# Camara QoD meeting - MOM-2023-01-27 + +*Januar 27th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Albert Wang (Huawei) +* Andrew +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Jignesh Sorathia (Spry Fox Networks) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Release v0.8.0 +* Release v0.8.1 +* Review of open PRs and issues +* AOB + +## Discussion + +| Agenda Item | Description | +| ----------- | ----------- | +| Release v0.8.0 | Release 0.8.0 done as agreed in last call.
                                                                  Release in GitHub: [https://github.com/camaraproject/QualityOnDemand/releases/tag/v0.8.0](https://github.com/camaraproject/QualityOnDemand/releases/tag/v0.8.0)
                                                                  Release branch: [https://github.com/camaraproject/QualityOnDemand/tree/release-0.8.0](https://github.com/camaraproject/QualityOnDemand/tree/release-0.8.0)
                                                                  Going forward we want to follow [Draft versioning guidelines doc](https://github.com/camaraproject/WorkingGroups/pull/123) (need to be finalized in Commonalities)
                                                                  Open issue/discussion: [API spec files and versioning](https://github.com/camaraproject/WorkingGroups/discussions/137) | +| Release v0.8.1
                                                                  Issue #105
                                                                  PR #106 | Issues addressed:
                                                                  • PR [#77](https://github.com/camaraproject/QualityOnDemand/pull/77) \- Fixed couple of typos
                                                                  • Issue #83 - Internal server error 500 missing for GET & DELETE procedures=> addressed with PR [#86](https://github.com/camaraproject/QualityOnDemand/pull/86)
                                                                  • Issue [#23](https://github.com/camaraproject/QualityOnDemand/issues/23) \- Consistent usage of notificationUri vs notificationUrldone with new issue [#88](https://github.com/camaraproject/QualityOnDemand/issues/88) and PR [#89](https://github.com/camaraproject/QualityOnDemand/pull/89))
                                                                  • Issue [#57](https://github.com/camaraproject/QualityOnDemand/issues/57) \- Update API documentation
                                                                  PR with update of changelog: [#106](https://github.com/camaraproject/QualityOnDemand/pull/106) ... ready to be merged (and done). | +| PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67)
                                                                  Issue [#38](https://github.com/camaraproject/QualityOnDemand/issues/38) | [Introduce 'qosStatus' and corresponding notification event to fix issue #38](https://github.com/camaraproject/QualityOnDemand/pull/67)
                                                                  • Open conversations from review marked as resolved (Emil)
                                                                  • **Target release v0.9.0**
                                                                  • **PR need to be rebased against main branch** **(branch dev-0.9.0 outdated and not in line with upcoming versioning guidelines)**
                                                                  • Documentation need to be updated according to the changes - within this PR or in separate one?
                                                                  • Thorsten will approach Emil as author of the PR with the above action items.
                                                                  | +| PR [#104](https://github.com/camaraproject/QualityOnDemand/pull/104) | [Align error format with Commonalities guidelines #104](https://github.com/camaraproject/QualityOnDemand/pull/104)
                                                                  • **Target releaase v0.9.0**
                                                                  • Additional reviewer: Patrice, Eric
                                                                  • To be merged as soon as possible (before #67), to get new error objects already in correct format
                                                                  | +| Issue [#34](https://github.com/camaraproject/QualityOnDemand/issues/34) | [Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34)
                                                                  • PR will be provided by Eric after PR #67 is done
                                                                  • **Target release: v0.9.0 - in general we will accumulate multiple changes within the next release, as there is currently no interest to implement an interims release**
                                                                  | +| Issue [#107](https://github.com/camaraproject/QualityOnDemand/issues/107) | [QoD Provider Implementation proposal - From Spry Fox Networks](https://github.com/camaraproject/QualityOnDemand/issues/107)
                                                                  • Slides presented by Ramesh are attached to the issue
                                                                  • Herbert will create the repo QualityOnDemand\_PI3 and will initially add Ramesh as code owner
                                                                  • Issue can be closed afterwards
                                                                  | +| Issue [101](https://github.com/camaraproject/QualityOnDemand/issues/101) | [List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (DT)
                                                                  • Recognized as an important functionality; DT is asked to provide a PR
                                                                  • Alignment with Design Guidelines necessary (pagination)
                                                                  | +| Issue [97](https://github.com/camaraproject/QualityOnDemand/issues/97) | [Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/issues/97)
                                                                  • Analysis done by Jose Luis Urien
                                                                  • Property names in snake\_case => Issue #90
                                                                  • Error format => PR #104
                                                                  | +| Issue [#96](https://github.com/camaraproject/QualityOnDemand/issues/96) | [Versioning of OAS yaml file in main branch between releases](https://github.com/camaraproject/QualityOnDemand/issues/96)
                                                                  • Waiting for Commonalities if and how API will should be versioned (independent of release versioning of the project)
                                                                  • **As interim solution we bump version number of QoD-API.yaml in main to 0.9.0-wip** (done)
                                                                  • Further discussion about versioning within Commonalities
                                                                  • Issue can be closed
                                                                  | +| Issue [#90](https://github.com/camaraproject/QualityOnDemand/issues/90) | [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90)
                                                                  • Request from Commonalities working group
                                                                  • First proposal for QoD from Jose Luis Urien
                                                                  • **Action item for all participants: Give feedback and opinions on the terminology and proposals for alternative names within the issue**
                                                                  • **Dedicated agenda item within next call**
                                                                  | +| Issue [#85](https://github.com/camaraproject/QualityOnDemand/issues/85) | [Content type for http error response should be of type "application/problem+json"](https://github.com/camaraproject/QualityOnDemand/issues/85) (SfnUser)
                                                                  • Discussed, can be closed. Further discussion within Commanalities.
                                                                  | +| Issue [#84](https://github.com/camaraproject/QualityOnDemand/issues/85) | [\[qod-api.yaml\]: IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/issues/84) (DT)
                                                                  • No change on API level, but mitigations in implementations?
                                                                  • DT will check for alternatives
                                                                  | +| Issue [#81](https://github.com/camaraproject/QualityOnDemand/issues/81) | [Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/issues/81) (DT)
                                                                  • Initial PR closed, waiting for PR #104 first
                                                                  • 4xx error code more suitable in most cases
                                                                  • **Target release v0.9.0**
                                                                  | +| Issue [#80](https://github.com/camaraproject/QualityOnDemand/issues/80) | [Inconsistencies in the spec](https://github.com/camaraproject/QualityOnDemand/issues/80) (SfnUser)
                                                                  • Discussed, inconsistent error messages around UEId can be addressed together with issue #34 (Eric)
                                                                  • Issue can be closed
                                                                  | +| Issue [#75](https://github.com/camaraproject/QualityOnDemand/issues/75)
                                                                  Issue [#31](https://github.com/camaraproject/QualityOnDemand/issues/31) | [Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/issues/75) (CapGemini)
                                                                  [Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) (DT)
                                                                  • Both issue are addressing same topic
                                                                  • Solution proposal needed
                                                                  | +| Issue [#47](https://github.com/camaraproject/QualityOnDemand/issues/47) | [need to include support for /PUT sessions](https://github.com/camaraproject/QualityOnDemand/issues/47)
                                                                  • Stale issue
                                                                  • Will be changed to backlog
                                                                  | +| Issue [#46](https://github.com/camaraproject/QualityOnDemand/issues/46) | [GET /sessions is missing status information](https://github.com/camaraproject/QualityOnDemand/issues/46)
                                                                  • Addressed within PR #67 (session life cycle and possible states)
                                                                  • Can be closed when PR #67 is done
                                                                  | + +## PRs that can be merged + +* PR #106 [CHANGELOG.md update for v0.8.1 release](https://github.com/camaraproject/QualityOnDemand/pull/106) + +## Issues that can be closed + +* Issue #105 [Release of v0.8.1 (fix release)](https://github.com/camaraproject/QualityOnDemand/issues/105) +* Issue #96 [Version of quod-api.yaml changed to 0.9.0-wip in main] +* Issue #107 [Repo QualityOnDemand created] +* Issue #80 +* Issue #85 + +## AOB + +* Next call is on February 10th. + * Dedicated agenda item: issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10.md new file mode 100644 index 0000000000000000000000000000000000000000..74df082830017b15a651f3e01b1dbaa11d7b6265 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-10.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - DRAFT MOM-2023-02-10 + +*February 10th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone)? +* Theohar (Hari) Konomi (TELUS) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Friman (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Shutting Qing (Huawei)? +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Further open Issues +* AOB + +## Open PRs + +* PR [#67](https://github.com/camaraproject/QualityOnDemand/pull/67) [Introduce 'qosStatus' and corresponding notification event to fix issue #38](https://github.com/camaraproject/QualityOnDemand/pull/67) + * Rebased to main, final review done and merged. + * Ready to merge? + * Fixed issues #38 and #46 + * Documentation need to be updated according to the changes => new issue +* PR [#104](https://github.com/camaraproject/QualityOnDemand/pull/104) [Align error format with Commonalities guidelines #104](https://github.com/camaraproject/QualityOnDemand/pull/104) + * Finally reviewed and ready to merge. + * There might be later additional alignment demand, e.g. when [WorkingGroups/issues/151](https://github.com/camaraproject/WorkingGroups/issues/151) is decided + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Notes from the discussion are documented in [comment](https://github.com/camaraproject/QualityOnDemand/issues/90#issuecomment-1427893395) +* Disucssions and polls will be opened by Herbert as noted. + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +Discussion: +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * DT will do a PR +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * and related issue [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * DT is currently testing a solution and might make a proposal here afterwards + * Further proposals are also welcome +* [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + * Eric will create a PR based on his proposal and the discussion + * He will consider to have private\_ipv4\_address and public\_ipv4\_address as top-level parameters in the object, both with potential additional information which the API consumer can provide to make them unambiguous + +## AOB + +* Next call is on February 24th. \ No newline at end of file diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24.md new file mode 100644 index 0000000000000000000000000000000000000000..bf9129d8c35927233b988208fb3a7231c7139af1 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-02-24.md @@ -0,0 +1,98 @@ +# Camara QoD meeting - MOM-2023-02-24 + +*February 24th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mayur Channegowda (Vodafone) +* Mihai Lazar (Dell) +* Mike Bowring (Spry Fox Networks) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Shuting Qing (Huawei) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* Issue #90 [Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Issue #34 [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* (NEW) [PR #124 Qod profiles](https://github.com/camaraproject/QualityOnDemand/pull/121) +* Further new and open Issues +* AOB + + +## Updates +* Provider implementation (DT) in review: [Implementation of 0.8.0 version](https://github.com/camaraproject/QualityOnDemand_PI1/pulls) + * PR will be merged as there are no comments so far +* Fix PR by Jose merged: [fix/restore-QosStatus-schema #116](https://github.com/camaraproject/QualityOnDemand/pull/116) + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Discussion on the polls (please vote before the call or during the discussion): + * [Preferred alternative for "ueID"? - device_info, device, or user_device](https://github.com/camaraproject/QualityOnDemand/discussions/117) + * No clear tendency yet, please continue to vote + * [Preferred alternative for "externalID" - external_id, network_access_identifier, ...?](https://github.com/camaraproject/QualityOnDemand/discussions/118) + * Clear tendency for "network access identifier" + * [Preferred alternative for "asId" - app_server_info, app_server, application_server, ...?](https://github.com/camaraproject/QualityOnDemand/discussions/119) + * Tendency towards "application server" + * [Preferred alternative for "uePorts"/"asPorts"? - *_ports, *_ip_ports, ...](https://github.com/camaraproject/QualityOnDemand/discussions/120) + * Tendency towards "_ports" over "_ip_ports" + * **Polls will kept open unti Friday, March 3rd, noon (UTC), please continue to provide your vote if not yet done** +* Sidenote: (camelCase vs snake_case) ongoing in Commonalities: https://github.com/camaraproject/WorkingGroups/issues/157 + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + +* Pull Request [#123 Update UeId definition in qod-api.yaml](https://github.com/camaraproject/QualityOnDemand/pull/123) +* Please provide your comments within the open PR (will be kept open at least until Friday March 3rd, and then until a cool down of 2 business days happened) +* Proposal to change paramater "port" with public IPv4 address into "public port" (Update: done by Eric) + +## PR [#124 Qod profiles](https://github.com/camaraproject/QualityOnDemand/pull/121) + +* Discussion: PR on backlog item #7 ... proposing a function to create QoS profiles + * The discussion started on the PR should first be done within one or two issues + * A dynamic creation of new QoS profiles shouldn't be offered to developers, but a discovery of QoS profiles offered by a network operator would be very helpful + * Also the possibility to get the QoS profiles as a machine readable object structure. The paramaters need an intensive discussion + * The current PR will be closed by Randy and he will summarize the discussion and learnings in one or two new issues which will probably superseed the existing issue #7. + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +New issues: +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * DT asked to do the PR + +As of last call: +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-02-24: no update +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * DT will do a PR +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * and related issue [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * DT is currently testing a solution and might make a proposal here afterwards + * Further proposals are also welcome + +## AOB + +* Next call is on March 9th diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10.md new file mode 100644 index 0000000000000000000000000000000000000000..97e149707bf18168cefd497bc22230b6ea01f61c --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-10.md @@ -0,0 +1,89 @@ +# Camara QoD meeting - MOM-2023-03-10 + +*March 10th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Jan Frimann (Ericsson) +* Jignesh Sorathia (Spry Networks) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Mike Bowring (Spry Fox Networks) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* Issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* PR [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Further new and open Issues +* AOB + +## Updates +* Lot of interest in Camara and GSMA Open Gateway on MWC in Barcelona. Several showcases with QoD API. + +## Qod relevant terms for Commonalities glossary + +* See issue [#90 Update commonalities glossary with qod-subproject relevant terms](https://github.com/camaraproject/QualityOnDemand/issues/90) +* **Request for all:** please review the definition proposed by Jose in https://github.com/camaraproject/QualityOnDemand/issues/90#issuecomment-1456609800. Jose will contribute the resulting definitions at latest on March 15th to Commonalities. +* New PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) prepared to execute the changes within API definition and documentation. Will be merged after the final decision about snake_case vs camelCase in Commonalities + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) + +* Pull Request [#123 Update UeId definition in qod-api.yaml](https://github.com/camaraproject/QualityOnDemand/pull/123) closed as the current discussion requires a new proposal. See continued discussion within the issue for Eric's proposal. +* Emil presented his discussion paper with concept and alternative API design, see [Discussion paper for Issue#34 and PR#123 #127](https://github.com/camaraproject/QualityOnDemand/pull/127) + * Eric asked to add a third scenario where both local/private UE address and observed/public UE address are collected on the device app and used within the QoD session create + * We will use the agreed term device instead of UE + * A decision between local/observed vs private/public IP might need a vote + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### New issues: + +* [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) + * Created by Randy as discussed within last call based on (now closed) PR #121 + * Some example QoS profiles would be helpful + * Discussion to be continued within the issue + +### Open issues: + +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * PR to be done (DT) +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and the discussion about terms within #90 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-03-10: no update +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) + +### Issues closed / to be closed: + +* [#81 Introducing error code 501 "Not Implemented"](https://github.com/camaraproject/QualityOnDemand/pull/81) + * PR done and merged +* [#75 Clarify usage of security scheme in call back](https://github.com/camaraproject/QualityOnDemand/pull/75) + * To be closed as duplicate to [#31 Ensure secure handling of callback URL], actual discussion in #31 + +## AOB + +* Next call will be on March 24th, 2 PM CET / 13:00 UTC (Please note: Europe will change on March 26th - after the next call - to daylight saving time) +* Agenda proposal will be created if possible at least one day in advance of the call as draft pull request diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24.md new file mode 100644 index 0000000000000000000000000000000000000000..6de0a4c3a0a0be67f5c9f327249f95a226db72f1 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-03-24.md @@ -0,0 +1,101 @@ +# Camara QoD meeting - MOM-2023-03-24 + +*March 24th, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Gareth Williams (GSMA) +* Georgia Souitari (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Shuting Qing (Huawei) +* Syed A Rehman (Verizon) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) +* Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Issue/Discussion [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open Issues +* AOB + * Next call + * Planning towards release v0.9.0 + +## Updates +* New/additional maintainer from Verizon: Mahesh Chapalamadugu [PR 132](https://github.com/camaraproject/QualityOnDemand/pull/132) + +## PR [Rename properties to new terms #129](https://github.com/camaraproject/QualityOnDemand/pull/129) +* Based on the decisions in [#90](https://github.com/camaraproject/QualityOnDemand/issues/90) +* Akos and Emil offered to do a review before merge +* PR will be kept open until Wednesday March 29th +* It's important to merge the PR soon as a prerequisite for the next PRs (the changes are across the complete YAML and documentation and merge conflicts would unavoidable) + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* Emil presented and explained the added scenario(s) within [UE IP address and ports in QoD.PA3.pdf](https://github.com/camaraproject/QualityOnDemand/files/11013180/UE.IP.address.and.ports.in.QoD.PA3.pdf) (attached at issue comment) +* Proposal is to ask developers to add all attributes they can observe (easily) and not make the minimum set dependent on network configurations +* Device port(s) might be neither helpful for device identification nor for (current simple) flow description - could be omitted completetly +* Port(s) should to with the IP addresses into the Device object - Emil will change the proposal accordingly +* Discussion to be continued within the issue (but should be concluded soon, see "Release Planning" in AOB) + +## Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Randy presented the updated proposal +* Throughput/bandwidth replaced with neutral term "rate" +* Q: intended for mobile and/or fixed - A: both +* Burstrate needs a description/definition of a burst (e.g. duration, percentage of time etc) +* Discussed if it would make sense to add a "type" of profile ('best effort' vs 'guaranteed') in addition to the attribute which allow to define theses characteristics (e.g. for easier search). Emil will have a closer look and might make a proposal into this direction. Term "GBR" should not be used as telco and mobile specific +* There was also a request to support (backwards compatibility with) the current QoS Profile enum + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### New issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * As per discussion on [camaraproject/WorkingGroups#61](https://github.com/camaraproject/WorkingGroups/issues/61), DT will provide basic tests with Cucumber framework using Java and Maven implementation + +### Open issues: + +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Proposal to omit default value of 86400 from YAML (leave it to network operator or developer), but keep the maximum of 86400 seconds + * PR to be done (DT, after PR #129 is merged) +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * In work with the (merged) PR #104 and #129 (see above) +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-03-24: no update +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) - therefore on hold in QoD + +### Issues closed / to be closed: + +* none + +## AOB + +* **Next Call** + * We will skip April 7th (Good Friday) + * The next call will be therefore on April 21st, 2 PM CEST / 12:00 UTC +* **Planning for release v0.9.0** + * Aim is to have a release of v0.9.0 before summer / within June + * There should be a release candidate (pre-release in Github terms) 4-6 weeks in advance to give implementators a chance to identify potential bugs/fixes necessary for the release, and adapt documentation and test cases + * The solutions for the two issues [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) and [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) should be at least part of the release v0.9.0 + * Herbert will create an issue with a proposed planning for the release (milestones and content) + diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21.md new file mode 100644 index 0000000000000000000000000000000000000000..7e2cbe4b6942d55a9f7e9b3c0f2ad0e261a48555 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-04-21.md @@ -0,0 +1,83 @@ +# Camara QoD meeting - MOM-2023-04-21 + +*April 21st, 2023* + +## Attendees + +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Chris Corcimiglia (CableLabs) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Ivan Nieto (Vodafone) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Mihai Lazar (Dell) +* Nuno Emanuel Rodrigues (Nos) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates +* [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) +* PR for [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* PR for [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open PRs and Issues +* AOB + * Next call + +## Updates +* Templates for issues and PRs agreed in Commonalities (see [Proposed Github issue and pull request templates #174](https://github.com/camaraproject/WorkingGroups/pull/174)) +* New issue: [Orga: Enable use of Issue and PR templates in QoD sub project #140](https://github.com/camaraproject/QualityOnDemand/issues/140) + +## Release Planning v0.9.0 +* Agreed as described in [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) +* Content will be the PR described below, target is to start the final review with the next call on May 5th +* Discussion of issue for v0.10.0 can start soon + +## Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34) +* PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) +* Please review the PR soon to allow resolving of comments before next call, comments to be documented within the PR +* Herbert will create votes (discussion items) for the remaining terminology discussions + +## Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* Please review the PR soon to allow resolving of comments before next call, comments to be documented within the PR + +## Further open PRs issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### Further open PRs and issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * Draft PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) + * Completion of the the PR planned for next week +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + * Will not be fixed, see [comment in issue](https://github.com/camaraproject/QualityOnDemand/issues/115#issuecomment-1515994592), to be closed +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/pull/97) + * Done with the (merged) PRs #104 and #129, to be closed +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-04-21: no update, stale issue +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) - therefore on hold in QoD + +### Issues closed / to be closed: + +* [#97 Alignment with API design guidelines](https://github.com/camaraproject/QualityOnDemand/issues/97) +* [#115 Default duration should be only an example](https://github.com/camaraproject/QualityOnDemand/issues/115) + +## AOB + +* The next call will be on May 5th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05.md new file mode 100644 index 0000000000000000000000000000000000000000..16892b09093216a4c1f98deb9f2d3a26de423c40 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-05.md @@ -0,0 +1,81 @@ +# Camara QoD meeting - MOM-2023-05-05 + +*May 5th, 2023* + +## Attendees (Incomplete) + +* ... +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Nuno Emanuel Rodrigues (Nos) +* Rafal Artych (Deutsche Telekom) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates and housekeeping +* PR for [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/pull/34) +* PR for [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* Further new and open PRs and Issues +* AOB + +## Updates and housekeeping + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * "Content will be the PRs described below, target is to start the final review with the next call on May 5th" + * Target is to have final review versions of PRs below until May 12th in Github + * New issue on documentation [Add documentation into API definition for release v0.9.0 ](https://github.com/camaraproject/QualityOnDemand/issues/144) + * Jose Luis Urien Pinedo volunteered, issue assigned + * Status of discussion within Commonalities on [Update API guidelines to add subscription/notification/event.md #173](https://github.com/camaraproject/WorkingGroups/pull/173)? => required for our issue [Ensure secure handling of callback URL #31](https://github.com/camaraproject/QualityOnDemand/issues/31) + * Rafal: aim in Commonality is to have final review/merge within next week. + + +## Issue #34 / PR #139 +* Issue [#34 Resolving ueAddr ambiguity when it is the UE private address](https://github.com/camaraproject/QualityOnDemand/issues/34) +* PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) +* Results of discussions/votes: + * [Vote: DeviceIpv4Addr object properties (from PR #139)](https://github.com/camaraproject/QualityOnDemand/discussions/141): Option 1 decided: `publicAddress`, `privateAddress` & `publicPort` + * [Vote: Rename of devicePorts property of CreateSession object](https://github.com/camaraproject/QualityOnDemand/discussions/142): decision to keep `devicePorts`for now +* Eric will update the PR based on the results, then ready for final review + +## Issue #124 / PR #138 +* Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* For discussion results see [PR comment](https://github.com/camaraproject/QualityOnDemand/pull/138#issuecomment-1537887796) + + +## Further open PRs issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +### Further open PRs and issues: + +* [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) + * PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) + * PR is in review - discussion will happen there. + +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * A regex is needed here which will sufficiently restrict the input ot valid IPv6 addresses => proposals are welcome + * Patrice recommened [https://regex101.com/](https://regex101.com/) as a good site to check regex patterns. + * 2023-05-05: no update, stale issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Need to be aligned with the discussion in Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) + * Result in Commonalities expected next week, impact on QoD API should go still into v0.9.0 if possible. + +### Issues closed / to be closed: + +* n/a + +## AOB + +* The next call will be on May 19th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19.md new file mode 100644 index 0000000000000000000000000000000000000000..da6c3a421402df23319426ff62d1b8338d32c34d --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-05-19.md @@ -0,0 +1,107 @@ +# Camara QoD meeting - MOM-2023-05-19 + +*May 19th, 2023* + +## Attendees + +* Andrew +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Karthik Sethuraman (?) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Updates and housekeeping +* Adding new maintainer +* Open PRs for v0.9.0 +* Further issues to be addressed for v0.9.0? +* Other issues (w/o backlog) +* Issues to be pulled from backlog for next release? +* AOB + +## Updates and housekeeping + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * Plan for today: + * Final decision which PRs will be merged for v0.9.0 (if not already done) + * Creation of prerelease of v0.9.0 (v.0.9.0-rc1, "Release Candidate") + * Purpose of the release candidate is that implementations can be started in order to identify bugs or other implementation obstacles + * For that the API definition and its structure is important. Descriptions can be changed independent of that. + * Note: PR [Updated method for identifying devices by IPv4 address #139](https://github.com/camaraproject/QualityOnDemand/pull/139) is already merged + + +## Adding new maintainer + +* Proposal to add Ramesh Shanmugasundaram (Spry Fox Networks, @sfnuser) to the list of Maintainers [PR](https://github.com/camaraproject/QualityOnDemand/pull/148) +* Unfortunately missed to address in the call ... current maintainers should vote with their approval to the [pull request #148](https://github.com/camaraproject/QualityOnDemand/pull/148) + +## PRs for v0.9.0 + +### Issue #125 / PR #138 +* Issue [#125 Adds service provider defined QoS profiles](https://github.com/camaraproject/QualityOnDemand/issues/125) +* PR [Create service provider defined QoS Profile #138](https://github.com/camaraproject/QualityOnDemand/pull/138) +* Discussion + * Q: can the current profile names (QOS_E, QOS_S, QOS_M, QOS_L) continued to be used. A: yes, that was the intention of keeping the format of QoSProfileName flexible. + * Three smaller change request to the PR raised (Randy noted them down). Including dealing with the warnings raised by swagger. Jose will help with these, as he has solved them also within PR #151 +* Jose, Eric, and Ramesh should approve that there comments are addressed +* Further comments on the descriptions to be postponed after the merge (via new issues). Target for now is to get the structure into the release candidate. +* Target is to merge within next week + +### Issue #144 / PR #151 +* Issue [Add documentation into API definition for release v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/144) +* PR [doc/update-spec-doc-issue-144 #151](https://github.com/camaraproject/QualityOnDemand/pull/151) +* New PR by Jose (@jlurien) +* Reviews by Randy, Emil and all other interested to review +* Review if possible within next week (until May 26th), so that Jose has a chance to addresse the comments before the next call. + +### Issue #133 / PR #134 +* Issue [Providing initial test case contribution #133](https://github.com/camaraproject/QualityOnDemand/issues/133) +* PR: [Pull Request for Initial QoD Cucumber Test contribution](https://github.com/camaraproject/QualityOnDemand/pull/134) +* Two approvals available, no open review comments +* Ready to merge. + * Note: Corrections can be done until final relase of v0.9.0 via issues and PRs, extensions via issues for later releases + + +## Further issues to be addressed still in v0.9.0? + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * See discussion within the issue + * Content discussion within Commonalities: [Unified Notfication/Event management #156](https://github.com/camaraproject/WorkingGroups/issues/156) seems to have concluded. UPDATE: issue is fixed, the respective [PR #173](https://github.com/camaraproject/WorkingGroups/pull/173) has been merged + * Herbert will ask DT team to check for the needed changes + +* [#146 Format 'ipv4' is more restrictive than the pattern in Data Type 'Ipv4Address'](https://github.com/camaraproject/QualityOnDemand/issues/146) + * Agreed solution is to omit the format strings "ipv4" and "ipv6" from the definitions of Ipv4Address and Ipv6Address + * Thorsten will create the PR for it (UPDATE: see [PR #153](https://github.com/camaraproject/QualityOnDemand/pull/153)) + + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +* [#84 IPv6-object will be generated instead of a String](https://github.com/camaraproject/QualityOnDemand/pull/84) + * 2023-05-05: no update, stale issue + * 2023-05-19: close issue as won't fix + + +## Issues to be pulled from backlog for next release? + +* see [https://github.com/camaraproject/QualityOnDemand/labels/QoD-backlog](https://github.com/camaraproject/QualityOnDemand/labels/QoD-backlog) + +### Issues closed / to be closed: + +* Issue #84, see above + +## AOB + +* Herbert will add a sentence within the README.md of the repository about the status of content in main (= work in progress, not yet released) +* The next call will be on June 2nd, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02.md new file mode 100644 index 0000000000000000000000000000000000000000..5c6a4ce9678760f674201b6f3cf69edd0ba35eb5 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-02.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - MOM-2023-06-02 + +*June 2nd, 2023* + +## Attendees + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jan Frimann (Ericsson) +* Jesus Gonzalez Tejeria (Vay) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Update and housekeeping +* PRs for v0.9.0 +* Further open issues (w/o backlog items) +* AOB + +## Updates and housekeeping + * New participant in the round: Jesus Gonzalez Tejeria from vay.io + * [Release Planning v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/136) + * We are behind the planned schedule ... we need to get the pending PRs merged as soon to be able to create the release candiate + * Update of README.md (PR #156) - ready to be merged after minor update for readability + +## PRs for v0.9.0 + +### Issue #125 / PR #138 +* Existing comments addressed, syntax linting done +* Final reviews to be done until end of Tuesday June 6th - the PR need to be merged to allow to resolve conflicts in PR #151 + +### Issue #144 / PR #151 +* One review so far, more would be preferred +* Added Emil and Randy who volunteered last time as reviewers, but all others are also invited to review +* Jose will update the PR after #138 is merged (to resolve conflicts) + +### Issue #133 / PR #134 +* Merged as agreed, issue #133 closed + +### Issue #154 and #157 / PR #155 +* Two proposals, no clear preference how to resolve https://github.com/camaraproject/QualityOnDemand/pull/155#discussion_r1212798906, tendency towards option 2 (more compact, compatible with swagger 2.0) +* Tendency to remove apiKey completely from API spec (and resolving issue #157 with that), Akos will check with Orange +* Akos will address the open points beginning of next week + +## Further open issues (w/o backlog items) + +* see [https://github.com/camaraproject/QualityOnDemand/issues](https://github.com/camaraproject/QualityOnDemand/issues) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * moved into backlog, as not fully addressed by updated notificiation handling +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * Supported as a good idea, Randy offered to make a proposal/pull request (Herbert will support if admin rights needed) + * Note: there is in the meantime also an issue within Commonalities (https://github.com/camaraproject/WorkingGroups/issues/232), both authors are connected + +### Issues closed / to be closed: + +* Issue #146 as done by PR #153 + +## AOB + +* Please help to get the release candidate v0.9.0 created (should be done within next call) +* The next call will be on June 16th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16.md new file mode 100644 index 0000000000000000000000000000000000000000..4c666d629ac12203de0afe7883c75209d2ee5574 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-16.md @@ -0,0 +1,110 @@ +# Camara QoD meeting - MOM-2023-06-16 + +*June 16th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* PR #151 - doc/update-spec-doc-issue-144 +* Preparation for v0.9.0-rc prerelease +* Issue #158 - Add linting GitHub actions +* Discussion of backlog issues, scope of release after v0.9.0 +* AOB + +## Updates and housekeeping + * Merged between the calls as agreed: + * PR [#163 Add oauth authorizationCode security to sensible endpoints](https://github.com/camaraproject/QualityOnDemand/pull/163) - fixed #161 + * PR [#155 Aligned notifications with guideline](https://github.com/camaraproject/QualityOnDemand/pull/155) - fixed #154 and #157 + +## Preparation for v0.9.0-rc prerelease + * Almost ready to create v0.9.0-rc, the release candidate of v0.9.0 + * Steps to create the release (similar for all releases) + * PR with updates of CHANGELOG.md and change of version in .yaml to v0.9.0-rc (instead v0.9.0-wip) + * Will be created by Herbert + * Review until eob Tuesday June 20th + * Merge commit of the PR will be tagged as v0.9.0-rc + * Via Github release feature, as pre-release in this case + * Release description will be copied from Changelog + * Proposal: no release branch for the pre-release + * Next commit after the release is setting the version within .yaml again to v0.9.0-wip + * Two or four weaks later the actual release v0.9.0, time to be used for + * Bug fixes, e.g. found by implementation teams + * Updates of documentation, e.g. clarifications, editorial fixes etc. + +## PR [#151 - doc/update-spec-doc-issue-144](https://github.com/camaraproject/QualityOnDemand/pull/151) + * PR is rebased to current main, comments are addressed + * Previous .md documentation file removed to avoid inconsistencies + * Discussion about QosStatus enum: + * The issue came up within comment in PR #155, but not solved there + * Option 1: use same enum within response bodies and events, explain differences (not all values will be currently used in events) in documentation + * Option 2: split current QosStatus enum in two, a new model "EventQosStatus" to be used within notification events + * Decision to go with option 2, as more flexible for future extensions + * Update: new PR [#167](https://github.com/camaraproject/QualityOnDemand/pull/167) created by Jose, will be merged on Monday + * PR merged and issue #144 closed + +## Issue [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * In work by Randy, PR to be expected for next call + * Cooperation with issue in Commanalities [#232 Extend the API guidelines with a concrete ruleset](https://github.com/camaraproject/WorkingGroups/issues/232) + * QoD sub project once again as pioneer + +## Discussion of backlog issues, scope of release after v0.9.0 + +* Definition of scope of v0.10.0 (or v1.0.0) should include input from the "Product Team" (in GSMA Open Gateway?) + * Process how demand from product perspective can come into the scope definition of next release to be clarified + * Jose will invite TEF colleague into next call to introduce the Product team + * Objective of the team is to ensure that defined APIs will be implemented by as many operators as possible with the same coverage of the API features + * Consensus that the ratio between value for developers/API consumers vs implementation effert for operators is an important criteria for the decisions which enhancements should go into the next release + * Beside "product requirements" there could be technical requirements which need to be addressed + +* General notion that the next release should have a focus on stability and should avoid breaking changes + +* Discussion of the issues currently within backlog + + * [#7 Add new endpoint in QoD API to request available qos_profiles](https://github.com/camaraproject/QualityOnDemand/issues/7) + * Base functionality done in v0.9.0, remaining functionality in #147 and #166 + * Original issue to be closed
                                                                  + * [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/pull/31) + * Security issue potentially not completely addressed within v0.9.0, Akos will create a new issue with the remaining points + * [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/pull/45) + * Functionality of NEF in Rel 16/17, unclear if implementions within operator cores are available + * Product demand to be clarified + * [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + * Demand and implementation effort to be clarified + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/101) + * Requests from developers known (to recover session IDs) + * Implementation be possible based on clientId used in OAuth authentication + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/pull/147) + * Derived from [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) above + * Demand and implementation effort to be clarified + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/pull/166) + * Derived from [#7](https://github.com/camaraproject/QualityOnDemand/issues/7) above + * Demand most likely, implementation effort to be clarified + +### Issues closed / to be closed: + + * Issue #144, fixed by #151 + * Issue #7, remaining issues within #147 and #166 + +## AOB + +* Topics for next call + * Status of release (candidate) v0.9.0 + * PR for #158 + * Discussion of product team request for next release +* The next call will be on June 30th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30.md new file mode 100644 index 0000000000000000000000000000000000000000..a886cf5e5cbbb040ca5c4096453c7dab3c6f1863 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-06-30.md @@ -0,0 +1,46 @@ +# Camara QoD meeting - MOM-2023-06-30 + +*June 30th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Akos Hunyadi (Deutsche Telekom) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Robert Ludovic (Orange) +* Theohar (Hari) Konomi (TELUS) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Discussion + +* Feedback to v0.9.0-rc … any bugs detected, when we are ready to do the actual release? + * Merged bug fix: priority integer format to int32 by @jlurien in https://github.com/camaraproject/QualityOnDemand/pull/175 + * Issue #174 agreed to change, Patrice will create the PR for it (update: see https://github.com/camaraproject/QualityOnDemand/pull/177) + * Notifications in callback … it would make sense to have a specific OAS for notifications to ease the generation of endpoints for the api consumer + * (Update: Robert and Patrice created an issue for that in Commonalities: https://github.com/camaraproject/Commonalities/issues/8) +* Discussion of the linting PR + * Timing -> v0.10.0 + * Herbert will check alignment with issue in commonalities + * Herbert has the necessary admin rights to deploy +* Scope of v0.10.0 … input from Open Gateway Product team - presentation by Jorge + * Brief introduction of the new WoW being define between GSMA and CAMARA, to provide requirements coming from GSMA Product stream into CAMARA. + + +## AOB + +* Topics for next call + * Creation of Release v0.9.0? +* The next call will be on July 14th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14.md new file mode 100644 index 0000000000000000000000000000000000000000..263739b9c10e400f1a92d4b9416a11b8d4dd6e31 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-14.md @@ -0,0 +1,74 @@ +# Camara QoD meeting - MOM-2023-07-14 + +*July 14th, 2023* + +## Attendees (not complete - add if needed) + +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Gareth Williams (GSMA) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Agenda + +* Open Issues +* Open PRs +* API Roadmap +* AOB + + +## Open Issues + +* [#174 Simplify Event Model for Notification in v0.9.0](https://github.com/camaraproject/QualityOnDemand/issues/174) + PR #177 is open, will get closed with it + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + PR #171 open for this, will be address after release of v0.9.0 + +* Other issues not discussed + +## Open PRs + +* [#177 fix(openapi): Add inheritance beetween Event and QosStatusChangedEvent](https://github.com/camaraproject/QualityOnDemand/pull/177) + Jose will revert towards the current NotificationEvent structure as defined in Design Guidelines (as proposed in https://github.com/camaraproject/QualityOnDemand/pull/177#issuecomment-1635517840) + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Will be addressed after release v0.9.0 is done. To be decided which linters will be activited at the start. Alignment with rule set which is in work at Commonalities tbd. + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + Not discussed, will be part of v0.10.0 + + +## API Roadmap + +### Release 0.9.0 + +* Release 0.9.0 ready to be released after merge of PR #177 +* Herbert will create respective issue and PR next week +* Randy reported that his team has successfully implemented the releace candidate and didn't encountered new issues + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and potentially from Notifiation/Subscription in Commonalities + * Current guideline not optimized for implicit notification subscription as in QoD API +* New features to be discussed in next call + * e.g. PATCH operation + +## AOB + +* The next call will be on July 28th, 2 PM CEST / 12:00 UTC +* Proposal to skip the call on August 11th (summer break) diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28.md new file mode 100644 index 0000000000000000000000000000000000000000..d725abe83e79c5b42e2a67bed4caf3c4f14a25ac --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-07-28.md @@ -0,0 +1,109 @@ +# Camara QoD meeting - MOM-2023-07-28 + +*July 28th, 2023* + +## Attendees (not complete - add if needed) + +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Herbert Damker (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + + +## Sub Project Management + +* Release v0.9.0 done +* Patrice Conil and Randy Levensalor added as additional maintainer of QoD Sub Project +* Shilpa Padgaonkar stepped back as code owner, Eric Murray and Randy Levaensalor added as codeowners +* Next meeting on August 11th: Eric will take the moderation + + +## Open Issues (including backlog) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) +To be replaced by an issue to adapt to changes out of #8 in Commonalities + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +Most potential customers are ok with a fallback to "default" class of QoS. Notion that implementation would be complex (at the moment) but limited market demand. To be kept in backlog. + + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) +PR #162 open. Agreed to implement first a minimum patch operation as described in comments. Behaviour behind patch of `duration` to be discussed first within the issue. Potentially an own endpoint necessary if the behaviour doesn't fit to a PATCH operation. + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +Syed mentioned the need to describe flows also with the protocol type (TCP, UDP). Use case examples to be added as comments. Might not require the introduction of IPFlowDescriptions. Decision if to pull from backlog based later. + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) +Nice to have functionality for developers. Requires to maintain relation of QoD session resources to resource owner based (based on access token). Should if possible get part of v0.10.0. therefore backlog label deleted. + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) +Two options seen in discussion: + * Use of comparisation operators on attributes. For that a definition in Commonalities (how to express in OAS) is pending. Challenge: need to be applied to complex object + * Additional GET endpoint which delivers based on a profile object with required/desired parameters a list of QoD profiles which are fulfilling the required quality parameters (if existing). This would require a specific comparisation logic. GraphQL could be a blueprint, but QoD sub project should introduce that only if there is broader demand across CAMARA sub project. Discussion to be continued within issue.

                                                                  + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + PR #171 open for this, Randy will break it down into smaller PRs in order to introduce linting in steps. + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) +Missed to discuss => next call + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +See comments within issue. Probably no change to the API, only relevant for implementation of certain profiles. Discussion to be continued within the issue. + + +* [#192 Change version number in main to v0.10.0-wip](https://github.com/camaraproject/QualityOnDemand/issues/192) Herbert will do a short PR with this change + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) Discussion points (to be continues within the issue): + * Main use would be to relate usage data from the network to a specific application of the API customer. Relevant for API customers who have different applications or application functions which they want to monitor regarding usage seperately. Assumption is that the application information will not come with the access token (as that would require different access token per application). + * This functionality (add application ID to the API call) might be relevant across several CAMARA APIs -> potentially issue to be opened in Commonalities. + +## Open PRs + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Randy will split the PR into several smaller PRs to introduce linting step by step + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + See discussion of issue #47 (update: changed status of PR to "draft" as we first want to discuss the logic behind patching `duration`) + + +## API Roadmap + +### Release 0.9.0 + +* Release 0.9.0 is done +* Prover implementations (PI) need to be updated, Herbert to create issues within the repositories + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notifiation/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) (minimal set of attributes which can be patched) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + + +## AOB + +* QoD maintainers are reqquested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on August 11th, 2 PM CEST / 12:00 UTC + * Herbert on vacation, Eric will moderate + diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11.md new file mode 100644 index 0000000000000000000000000000000000000000..46c9de9147e792c190bb41a5cb448be67c461bbe --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-11.md @@ -0,0 +1,133 @@ +# Camara QoD meeting - MOM-2023-08-11 + +*August 11th, 2023* + +## Attendees + +* Eric Murray (Vodafone) +* Thorsten Lohmar (Ericsson) +* Patrice Conil (Orange) +* Emil Zhang (Ericsson) +* Randy Levensalor (CableLabs) +* Toshiyasu Wakayama (KDDI) +* Syed A Rehman (Verizon) +* Jose Luis Urien Pinedo (Telefonica) +* Akos Hunyadi (Deutsche Telekom) +* Rafal Artych (Deutsche Telekom) +* Babu Narayan (Nabstract) +* Bhabani Panda (Meta) +* Vidhi Mehta (Comviva) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* Release v0.9.0 done +* Next meeting on August 25th + +## Open Issues (including backlog) + +### Issues discussed during meeting + +* [#199 QoD 0.9 - inline documentation problem](https://github.com/camaraproject/QualityOnDemand/issues/199) +
                                                                  Proposal to include link to Swagger editor or ReDoc formatted version of the API specification within the release notes + - General agreement that this was a good idea + - **Decisions:** + - Add inline links to Swagger and Redoc formatted version of API definition to both release notes and README.md (for latest release) + - Raise with Commonalties to make this a requirement for all APIs + - Eric to request Herbert update release notes and README for QoD + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) +
                                                                  Automatic linting of API specification before being merged into repository + - **Decisions:** + - Agreed that this was a good time to test linting on v0.10.0-wip before this is further modified + - Randy to look to implement this first for simple formatting update (prettifying) to understand how linting tools can be applied to the repository. If insufficient permissions for this, Randy will contact Herbert. + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) +
                                                                  Main use would be to relate usage data from the network to a specific application of the API customer. Relevant for API customers who have different applications or application functions which they want to monitor regarding usage separately. Assumption is that the application information will not come with the access token (as that would require different access token per application). + - Syed gave a [presentation](https://github.com/camaraproject/QualityOnDemand/blob/6d6cca9162f491db6b5ff501d1bce80ece0ab900/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx) on this issue. The following clarifications and comments were made: + - Relationship between API consumer Id, application server IP address, and proposed appId is not necessarily one-to-one + - API consumer may be managing multiple application servers + - Application servers may have more than one IP address, or share a single IP address with multiple applications + - An alternative to explicitly identifying the application by appId would be for each application to be identified by a separate OAuth key / token + - For some API consumers, however, this could be unmanageable + - This solution would also be effectively proprietary, requiring the OAuth key identity to be extracted and passed to the API using, for example, a header + - If an explicit appId was passed via the API, validating this would be an issue + - Some workflow examples of appId validation and error cases would be useful + - For mobile networks, appId would map to aspId (or sponsorId) of NEF. There is no equivalent mapping for fixed networks, so use of appId would likely be proprietary. + - Accessing records by appId would remain proprietary for each API implementor, with no plans to introduce additional CAMARA APIs for this + - This functionality (add application ID to the API call) might be relevant across several CAMARA APIs -> potentially issue to be opened in Commonalities. + - **Decisions:** + - Syed to make proposal on how appId would be introduced into the QoD API definition, and to give additional details on how it would be validated and used. + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) +
                                                                  Previous discussion of options: + - Use of comparison operators on attributes. For that a definition in Commonalities (how to express in OAS) is pending. Challenge: need to be applied to complex object + - Additional GET endpoint which delivers based on a profile object with required/desired parameters a list of QoD profiles which are fulfilling the required quality parameters (if existing). This would require a specific comparison logic. GraphQL could be a blueprint, but QoD sub project should introduce that only if there is broader demand across CAMARA sub project. Discussion to be continued within issue. + +
                                                                  Issue was further discussed during meeting: + - Probably only required if the number of QoS profiles is large + - For mobile networks, this is unlikely given the difficulties radio networks have in balancing multiple different QoS requirements + - For fixed networks, it is more likely that the number of offered profiles will eventually be large, but not for initial deployments of the API + - Exact requirements still not clear + - Do we need ranges, or just greater than (or equal) or less than (or equal) to specified value? + - API definition support for filtering by ranges / inequalities is currently being discussed in [Issue #10](https://github.com/camaraproject/Commonalities/issues/10) in Commonalities. + - **Decisions:** + - Probably not required for v0.10.0. Randy to consider when this might be required. + - Randy to formalise requirements so that they can be fed into Commonalities and taken into account in any modified filtering scheme + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - Randy proposed that DSCP be an explicit parameter of a QoS profile. Probably a single parameter applying to both upstream and downstream traffic. + - Not clear how this parameter would apply to mobile network. Mobile network operators / equipment vendors input welcome. + - Parameter could not be enforced outside of CSP's won network + - **Decisions:** + - Randy to make proposal to add DSCP as an explicit but optional parameter of the QoS profile + - Mobile network operators / equipment vendors to comment in the issue of the value of this for mobile networks + +### Issues not discussed during meeting + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs - Not directly discussed during meeting + +* [#171 First pass for including linting for pull requests](https://github.com/camaraproject/QualityOnDemand/pull/171) + Randy will split the PR into several smaller PRs to introduce linting step by step + +* [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162) + See discussion of issue #47 (update: changed status of PR to "draft" as we first want to discuss the logic behind patching `duration`) + + +## API Roadmap + +### Release 0.10.0 + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) (minimal set of attributes which can be patched) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Probably excluded from next release + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + + +## AOB + +* QoD maintainers are requested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on August 25th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25.md new file mode 100644 index 0000000000000000000000000000000000000000..2dc0c348fd97951911a1e6cb2a97d6054584f9a2 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-08-25.md @@ -0,0 +1,106 @@ +# Camara QoD meeting - MOM-2023-08-25 + +*August 25th, 2023* + +## Attendees (not complete) + +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Robert Ludovic (Orange) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshiyasu Wakayama (KDDI) +* ... + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* no updates + +## Open Issues (including backlog) + +### Issues discussed during meeting + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) +
                                                                  Automatic linting of API specification before being merged into repository + - Randy added as a codewoner, will allow him to merge respective PRs + - Stepwise approach + - Swagger editor validator (PR #206) merged during the call + - Megalinter (PR #215) as netx step + - DT will take of JAVA linting + + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - Presentation update uploaded: https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx + - Jose: close relation with identity discussions within Identity&Consent and GSMA + - Syed to provide a proposal as a PR + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - Most probably only few profile within mobile networks, probably more in fixed networks upcoming + - Decision: not in scope for v0.10.0, we will wait until a larger number of profiles are in use + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - no update, discussion to be continued in the issue + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - depending on authentication/identity of API consumer + - DT considers to make a proposal + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - Discussion + - Change of session duratin should be done with an explicit endpoint which will allow to include the necessary logic behind. "Patching" the duration would be unclear regarding impacts. + - Patching notificationAuthToken: to be reconsidered after new notification/event approach is concluded in Commonalities (including security concept) + - Decision + - PR for new endpoint to change session duratin (Emil) + - no further PATCH operation as of now + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - waits for general solution in Commonalities. + - request to participate in the discussion there (especially https://github.com/camaraproject/Commonalities/pull/56) + + +### Issues not discussed during meeting (backlog items) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs + +* not directly discussed within the meeting + +## API Roadmap + +### Release 0.10.0 (only updated) + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47 (will be realized as new endpoint for change of session duration, no PATCH operation for a session) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Excluded from next release + * [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) => changed back to backlog item + + +## AOB + +* QoD maintainers are requested to actively support the resolution of issues which the sub project raised in Commonalities. +* The next call will be on September 8th, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08.md new file mode 100644 index 0000000000000000000000000000000000000000..ecbf8c4c32e29d6456810a4c923ee1d65550cf32 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-08.md @@ -0,0 +1,115 @@ +# Camara QoD meeting - MOM-2023-09-08 + +*September 8th, 2023* + +## Attendees (potentially not complete) + +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom) +* Jason Mei (Whale Cloud) +* Joachim Dahlgreen (Ericsson) +* Jorge Garcia Hospital (Telefonica) +* Patrice Conil (Orange) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Ludovic Robert (Orange) +* Thorsten Lohmar (Ericsson) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Sub Project Management +* Open Issues +* Open PRs +* API Roadmap +* AOB + +## Sub Project Management + +* From TSC (Herbert, Eric): + * TSC participants and all active maintainers are asked to review and comment on the currently open issues and PR for event and notification structure in Commonaltities - especially issue pull request [Update DG with use of callbacks & cloudEvents #56](https://github.com/camaraproject/Commonalities/pull/56). The PR need to be closed soon and has to adapted by the sub project + * For other points from TSC see minutes of TSC which will be added to https://github.com/camaraproject/Governance/tree/main/documentation/MeetingMinutes/TSC + +* Introduction of linting (was issue #158) + * Linting of YAML file was introduced with PR [Megalinter initial #207](https://github.com/camaraproject/QualityOnDemand/pull/207). The PR contains also the (minor) changes within qod-api.yaml to adapt to linting. Beside correction of spaces one example needed to be corrected and URL variables to be replaced with concrete examples. + * During last two weeks two small changes to Megalinter configuration + * PR #215 will enable in addition the linting of Java files + + +## Discussion of Open Issues + +### Issues discussed during meeting + +* [#209 Add 400 - Bad Request for an invalid sessionId GET + DELETE /sessions/{sessionId}](https://github.com/camaraproject/QualityOnDemand/issues/209) + * PR ready to be merged, adding generic 400 for the two endpoints + * The change will go into v0.10.0, patch for v0.9.1 only if someone their is demand for that + +* [#204 Move the "description" out of "allOf"-declaration](https://github.com/camaraproject/QualityOnDemand/issues/204) + * PR #205 ready for final review + * Swagger editor and redoc are still showing the right descriptions with the proposed approach; "allOf" declaration as workaround still needed even with only one element (otherwise the generic description of the referenced schema will be shown) + * AP Randy to do a final check with his development team before approval + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) and updated presentation in https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/SupportingDocuments/Presentations/Sponsor%20or%20App%20Id%20proposal.pptx + - [PR #217](https://github.com/camaraproject/QualityOnDemand/pull/217) provided by Syed, first comment from Eric available + - Issue and PR open for discussion, labels added accordingly + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + - Discussion of the latest comments on the issue + - AP Randy to summarize the results of the discussion within the issue itself + +* [#158 Add linting GitHub actions](https://github.com/camaraproject/QualityOnDemand/issues/158) + * Already closed, see above in "Sub Project Management" + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - previous discussion and decisions see [MOM-2023-08-11.md](https://github.com/camaraproject/QualityOnDemand/blob/main/documentation/MeetingMinutes/MOM-2023-08-11.md) + - moved into backlog, excluded from v0.10.0 scope + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - no update + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - To be replaced with new issue which fits to Emil’s PR + - AP Herbert: create issue and relink the PR + - PR [#216 Extend or reduce session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) opened as a proposal + - Discussion if the operation should allow also to reduce the session duration or only extend it ... some voices to allow only extend. For reduction of session duration there should be an use case presented, which justifies the effort to implement the logic (especially if the resulting duration is less then the already elapsed duration) + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - waits for general solution in Commonalities + - request to participate in the discussion there (especially https://github.com/camaraproject/Commonalities/pull/56) + + +### Issues not discussed during meeting (backlog items) +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + +## Open PRs + +* all open PRs are already mentioned above + +## API Roadmap + +### Release 0.10.0 (only updated) + +* September-October 2023? (as for DeviceStatus 0.6.0) +* Focus on stabilization of API definition, e.g. introduction of linting +* Changes expected from Authn/Authz discussion in Identity & Consent and from Notification/Subscription in Commonalities +* New features so far based on discussed issues + * [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) - will be realized as new endpoint for change of session duration, no PATCH operation for a session planned anymore + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) (incl authorization concept) +* Candidate features + * [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) +* Excluded from next release + * Backlog Issues: #166, #147 (see last MoMs), #51, #45 + * Note: #31 (Ensure secure handling of callback URL will be addressed by new notification structure) + +## AOB + +* The next call will be on September 22nd, 2 PM CEST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22.md new file mode 100644 index 0000000000000000000000000000000000000000..db3835fe316561364e634a897f28613c8302177d --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-09-22.md @@ -0,0 +1,97 @@ +# Camara QoD meeting - MOM-2023-09-22 + +*Friday, September 22nd, 2023* + +## Attendees + +* Eric Murray (Vodafone, Moderator) +* Rafal Artych (Deutsche Telekom) +* Patrice Conil (Orange) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Emil Zhang (Ericsson) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Submitted as a replacement for [#162 Add PATCH operation](https://github.com/camaraproject/QualityOnDemand/pull/162), which is now closed + * Based on feedback received, scope is limited to extending session durations only. PR remaned. + * Two discussion points remain open with the PR: + * New endpoint requires an associated security scheme (now agreed) + * Should extending session durations beyond the maximum allowed for a new session (currently 1 day) be allowed? + * **If participants have a view on whether sessions can be extended beyond 1 day maximum duration, please comment in the associated issue** + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Two discussion points currently open + * Exact relationship between `applicationConsumerId` and the end user, API consumer and other actors in the API transaction is not clear. In particular, for three-legged authentication, should the `applicationConsumerId` be provided at the authorisation stage (in the same way as, for example, `phoneNumber`)? + * Should `applicationConsumerId` be a "top level" parameter in the `CreateSession` schema, or part of the `ApplicationServer` schema? + * **Syed to clarify exact scope of `applicationConsumerId`, and maybe consider renaming** + * **Participants with a view on either open point, or with additional open points, to comment in the associated issue before the next meeting** + +## Discussion of Open Issues + +### Issues For Next Release + +* [#221 Change event structure and notification according to Design Guidelines changes](https://github.com/camaraproject/QualityOnDemand/issues/221) + * A revised model for callbacks is close to being agreed within Commonalties (see Commonalities [#56](https://github.com/camaraproject/Commonalities/pull/56)) + * The revised model must be adopted by QoD for release 0.10.0 + * **Jose Luis volunteers to prepare the necessary PR** + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * Still not clear if the proposed new parameter is relevant for mobile networks + * Waiting for Randy to summarize the results of the discussion and make a specific proposal for required API changes and their impact on API behaviour + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - Akos to update issue with DT's current view on this proposal now that they have feedback from developers + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - Use case of refreshing OAuth token for callbacks remains open + - Jose to review new approach to callbacks being defined by Commonalities to see if this issue is covered there. If not, this requirement can continue to be discussed within the issue. + +* [#209 Add 400 - Bad Request for an invalid sessionId GET + DELETE /sessions/{sessionId}](https://github.com/camaraproject/QualityOnDemand/issues/209) + * Closed by PR [#210](https://github.com/camaraproject/QualityOnDemand/pull/210) + +* [#204 Move the "description" out of "allOf"-declaration](https://github.com/camaraproject/QualityOnDemand/issues/204) + * Closed by PR [#205](https://github.com/camaraproject/QualityOnDemand/pull/205) + +### Backlog Issues + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + - Stale issue + - Akos to check on status within DT and whether this is still required + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - No updates on this issue + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + - No requirement for this capability yet identified + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + - No update on this issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - To be reviewed when new callback approach is adopted. To remain open for now. + + +## API Roadmap + +### Release 0.10.0 + +* Not discussed + +## AOB + +* The next call will be on Friday October 6th, 14:00 CEST / 13:00 BST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06.md new file mode 100644 index 0000000000000000000000000000000000000000..758f3506bba42f228c00e17b2c0e4d0584088593 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-10-06.md @@ -0,0 +1,112 @@ +# Camara QoD meeting - MOM-2023-10-06 + +*Friday, October 6th, 2023* + +## Attendees + +* Herbert Damker (Deutsche Telekom, Moderator) +* Eric Murray (Vodafone) +* Rafal Artych (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) +* George Haddad (Liberty Global) + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Housekeeping +* Release 0.10.0 +* Open PRs +* Open Issues +* AOB + + +## Housekeeping + +* Next call on Oct 20th collides with OGW f2f meeting in London. Decided to keep the call. + +## API Roadmap + +### Release 0.10.0 + +* Focus of the release v0.10.0 is to adapt to the current changes within Commonalities +* Enhancement which are ready will be taken into the release, but we don't wait for them. They can go into a following release. +* Background is that some operators (e.g. DT) need to decide which version to implement for customers. v0.9.0 would require breaking changes shortly afterwards to get compliant to Commonalities (e.g. event and notification structure) +* If possible: PRs for v0.10.0 ready until next call (Oct 20th), RC ready in the call afterwards (Nov 3rd) + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Open discussion point from previous meeting: + * Should extending session durations beyond the maximum allowed for a new session (currently 1 day) be allowed? + * Discussion result: + * New remaining session duration should not exceed the 1 day maximum duration (remaining duration + extension <= 86400 seconds) + * If new remaining session duration would exceed 86400 seconds, no error should be raised but session duration set to value where the remaining session duration is about 86400 seconds + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Two discussion points are still open + * Naming of the identifier should be changed to express the relationship to API consumer (identity within access token). According to Syed the main purpose is to allow the API consumer to track the API and resource usage more granular then on level of API consumer identity only. An API consumer could have different application functions which they might want to see differentiated on a bill. "applicationConsumerId" is misleading here. + * If the Id is related (one to one?) to an application (server) it would make sense to move it into the applicationServer object. But that might be specific to QoD API and not apply to other APIs. The enhancement should be discussed within Commonalities first. + * **Syed to clarify exact scope of `applicationConsumerId`, and maybe consider renaming. Also to clarify the expecation of (usage) data collected related to the Id by the network (to allow estimation of implementation effort)** + * **Syed to address and drive the topic in Commonalities as it might be relevant for further APIs, not only QoD** + * **Participants with a view on either open point, or with additional open points, to comment in the associated issue before the next meeting** + +## Discussion of Open Issues + +### New Issue since last meeting + +* [#223 Operation tags in global tags element](https://github.com/camaraproject/QualityOnDemand/issues/223) + * Tags are relevant to sort operations e.g. within swagger editor (see [View it on Swagger Editor](https://editor.swagger.io/?url=https://raw.githubusercontent.com/camaraproject/QualityOnDemand/release-0.9.0/code/API_definitions/qod-api.yaml)) + * **Rafal to propose necessary change to fulfill the linting rule as a PR** + +### Issues For Next Release + +* [#221 Change event structure and notification according to Design Guidelines changes](https://github.com/camaraproject/QualityOnDemand/issues/221) + * A revised model for callbacks is agreed and merged within Commonalties (see Commonalities [#56](https://github.com/camaraproject/Commonalities/pull/56)) + * The revised model must be adopted by QoD for release 0.10.0 + * **Jose Luis volunteers to prepare the necessary PR (update after call: [PR #224](https://github.com/camaraproject/QualityOnDemand/pull/224) available for review)** + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * No update, waiting for Randy to summarize the results of the discussion and make a specific proposal for required API changes and their impact on API behaviour + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + - DT team is working on a proposal, Akos will provide a PR when ready (might not make it into v0.10.0) + - Jose has commented in the issue. TEL is working on a proposal, e.g. elaborating the requirements around which sessions are allowed to be discovered by certain client, which filters may apply to that query, e.g. searching for sessions for certain MSISDN + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + - No update, previous comments still valid + - Use case of refreshing OAuth token for callbacks remains open + - Jose to review new approach to callbacks being defined by Commonalities to see if this issue is covered there. If not, this requirement can continue to be discussed within the issue. + + +### Backlog Issues (only partly discussed) + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + - Stale issue + - Herbert: it isn't a DT issue or requirement, it was originally brought up by Ericsson and just reported by DT. + - There are no requirements for this capability yet identified + +* [#147 Extend the query capabilities for Qos Profiles](https://github.com/camaraproject/QualityOnDemand/issues/147) + - No updates on this issue + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + - No requirement for this capability yet identified + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + - No update on this issue + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + - To be reviewed when new callback approach is adopted. To remain open for now. + + + +## AOB + +* Note: Next call will collide with OGW F2F meeting in London, some participants might be not available +* The next call will be on Friday October 20th, 14:00 CEST / 13:00 BST / 12:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03.md new file mode 100644 index 0000000000000000000000000000000000000000..d41c3d68fbcc6a740df6472926cc534c5fe55afb --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-03.md @@ -0,0 +1,83 @@ +# Camara QoD meeting - MOM-2023-11-03 + +*Friday, November 3rd, 2023* + +## Attendees + +* Herbert Damker (Deutsche Telekom, Moderator) +* Andrew Wajs (Scenera) +* Emil Zhang (Ericsson) +* Eric Murray (Vodafone) +* Rafal Artych (Deutsche Telekom) +* Akos Hunyadi (Deutsche Telekom) +* Jose Luis Urien Pinedo (Telefonica) +* Thorsten Lohmar (Ericsson) +* Andrew Wajs (Scenera) +* Joachim Dahlgreen (Ericsson) +* Syed A Rehman (Verizon) +* Toshi Wakayama (KDDI) +* Ramesh Shanmugasundaram (Spry Fox Networks) + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Open Issues +* Release v0.10.0 +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Ready for final review => Action point for all to review and approve or comment + * Please have a specific view on the description, if it is understandable + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * It is still open when and how the `applicationId` will be agreed between API client and API provider but there is common understanding that this need to be an agreed identifier + * According to Syed this has to happen within an application onboarding process between the operator and the application service provider + * With that there is a relation to the Onboarding Playbook under discussion within GSMA Open Gateway business stream and especially with the "Operate APIs" currently in design phase within TM Forum to support the onboarding process in case of an aggregator between application service provider and operator + * It is also possible that the application will be identified within the authorization token coming with the API call, e.g. if different client IDs are used per onboarded application + * The above points need to be clarified before we add the identifier to the API parameters + * Syed will get in contact with the colleagues within the Operate API working group in TMF, Jose will provide contacts + * Decision: + * The requirement to have an identifier which allows to track the usage per application will be kept + * The PR will be set into draft status until the above questions are clarified + +[#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) - Issue 221 + * The PR should reflect the latest definitions within CAMARA Design Guidelines, ready for final review + * Jose proposed to add Ludovic Robert as reviewer (done) + * Request to all to review asap + +[#227 Adding global tags element](https://github.com/camaraproject/QualityOnDemand/pull/227) + * Decision to use "Title Case" for all tags for now and adapt potentially later if Commonalities decides differently (open issue [#80](https://github.com/camaraproject/Commonalities/issues/80)) + * With this change the PR will be ready for review + +[#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) - Issue #101 + * PR still in draft, but should be - if possible - be part of v0.10.0 + * Decision about which sessions to be returned back to the API client: for now we define it generic/abstract as "all sessions the presented authorization token has (read) access to". That allows to define further details if there are changes within the authorization flow + * Request to make the PR ready for final review + +## New Issues + +* [#230 Single IPv6 addresses within device]() + * New issue from Jose + * IPv6 address most probaly can not covered correctly by a regex + * Note: At least for some mobile networks (e.g. DT Germany) already the prefix is related to an unique and will be match to identify the device + +All other open issues either in work (see above) or not considered for v0.10.0 and therefore not discussed due of time. + +### Release 0.10.0 + +* Release candidate v0.10.0 to be created after the above discussed PRs are reviewed and merged: + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) + * [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) +* Target is to get these PRs reviewed and merged until next call on Nov 17th, so that we can decide the release candidate there +* Release candidate will be the starting point for implementations. Release to be expected about 2 or 4 weeks later. +* Herbert will create the issue with this release plan + +## AOB + +* The next call will be on Friday November 17th, 14:00 CET / 13:00 BT / 13:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17.md new file mode 100644 index 0000000000000000000000000000000000000000..a32236c28da28ef782929604df7b2b43fbdc7d83 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-11-17.md @@ -0,0 +1,100 @@ +# Camara QoD meeting - MOM-2023-11-17 + +*Friday, November 17th, 2023* + +## Attendees (probably incomplete) + +* Andrew Wajs (Scenera) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Jorge Garcia Hospital (Telefonica) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Toshi Wakayama (KDDI) + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Open PRs +* Discussed Issues +* Release v0.10.0 +* AOB + +## Discussion of Open PRs + +* [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) (Associated Issue [#220 Change duration of an active session](https://github.com/camaraproject/QualityOnDemand/issues/220)) + * Tag of operation updated (belongs to `QoS Sessions`) + * Description updated + * ACTION ITEM - final review by code owners for approval until Wed Nov 22nd + +* [#217 issue_194_PR](https://github.com/camaraproject/QualityOnDemand/pull/217) (Associated Issue [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * PR in draft status, not discussed + +[#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) - Issue 221 + * Data object optional within Event base class (in line with other APIs using CloudEvents). Can be adapted if there is a global change within guidelines + * ACTION ITEM - final review by code owners for approval until Wed Nov 22nd + +[#227 Adding global tags element](https://github.com/camaraproject/QualityOnDemand/pull/227) + * PR is merged and issue closed + +[#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) - Issue #101 + * PR still in draft, and it is unclear if the open points can be resolved in time for v0.10.0 (see below ... release candidate should be created end of next week which require to have the PR ready for review start of the week) + * Still optional for v0.10.0. + * Discussions: + 1. Can the endpoint deliver (A) all sessions created by the requesting API consumer or (B) only the ones for the user resource within the (3-legged) token? (in other word: does the endpoint later require 2-legged or 3-legged token, in case 3-legged token will (later) be required to create a QoD session resource) + * For now the assumption is that the operation delivers all sessions which are authorized by the token (all sessions created for 2-legged, only user sessions for 3-legged). Decision about needed token is postponed. + 2. Should the operation deliver the full session information or just the session ids? + * Result of the discussion: return the full session information + * Rational: this is the more developer friendly option, as otherwise the API consumer would need to call getSession one by one to find the information they are looking for. From privacy perspective has the API consumer provided and seen all personal information already during the respective session creations. It should be enough that the API consumer was authorized to create the sessionId(s) to assume consent for the get operation. + 3. Is paging needed or not? + * That depends on the answer to point 1. If only the sessions for one user device are delivered is no paging necessary. If all sessions for an API consumer are delivered then paging might be needed to avoid excessive data within the response + 4. Filtering by `device` or `phoneNumber` (Added after the call, comment from Randy https://github.com/camaraproject/QualityOnDemand/pull/228#discussion_r1397522143) + * Potentially the discussions can be not be closed for v0.10.0, in this case the feature will be postponed to the next release. + +[#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) + * PR creates the directory `Test_definitions` and copies the existing .feature file into this directory. + * The question what should happen with the JAVA code within the /cucumber folder can not be answered within the context of the PR + * It is about the general questions if such code (to execute the test definitions) could be provided centrally for all APIs, and if yes, where (e.g. in Commonalities or Release Management) + * ACTION ITEM: Rafal to create an issue in Commonalities for an initial clarification + * The PR itself is ready for final review by code owners (and does not change the API definition). Will go into v0.10.0 + + + +## Discussed Issues + +* [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) + * Agreed to follow the proposal within Jose's comment https://github.com/camaraproject/QualityOnDemand/issues/230#issuecomment-1812335931 - only formats allowed in device would be those considered in [JSON-schema](https://json-schema.org/understanding-json-schema/reference/string#ip-addresses) (`ipv4` and `ipv6`). + * `devicePorts` might need be (re)defined later. + * ACTION ITEM: Jose to create a PR asap, so that it can potentially go into v0.10.0 + +[#231 Error behaviour when session cannot be created due to "time cap" limitation](https://github.com/camaraproject/QualityOnDemand/discussions/231) + * Opened as discussion, not as an issue - hasn't received any attention as a discussion + * The question is actually not QoD specific, but relevant for all APIs (as there could be a cap of agreed number of API calls or a lack of prepaid money) + * ACTION ITEM: Jose to create issue in commonalities + + +All other open issues either in work (see above) or not considered for v0.10.0 and therefore not discussed due of time. + +## Release plan for 0.10.0 + +* **The release candidate for v0.10.0 should be created at end of next week (Friday Nov 23rd) to have enough time to validate the release candidate by implementing operators and do the actual release of v0.10.0 at latest before year end break.** +* The following PRs MUST be included in the release candidate v0.10.0 + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) + * [#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) +* The following PRs COULD be included within the release candidate if finalized in time + * [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) + * Yet to be done PR for issue [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) +* Release candidate will be the starting point for implementations. Release to be expected about 2 or 4 weeks later. +* Between release candidate and release only bug fixes and updates of documentation will be done on the API spec. +* ACTION ITEM: Herbert will create the issue with this release plan and prepare the changes to CHANGELOG.md + +## AOB + +* The next call will be on Friday December 1st, 14:00 CET / 13:00 BT / 13:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01.md new file mode 100644 index 0000000000000000000000000000000000000000..2ddc05def621db627b2d2d051c5bf929596db951 --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-01.md @@ -0,0 +1,115 @@ +# Camara QoD meeting - MOM-2023-12-01 + +*Friday, December 1st, 2023* + +## Attendees (probably incomplete) + +* Akos Hunyadi (Deutsche Telekom) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Jan Frimann (Ericsson) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Patrice Conil (Orange) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Merged PRs & Release Candidate v0.10.0 +* Discussed Issues +* AOB + +## Merged PRs & Release Candidate v0.10.0-rc + +* The following PR were merged since the last meeting: + * [#216 Extend session duration](https://github.com/camaraproject/QualityOnDemand/pull/216) after final review + * [#224 Align event notification with CloudEvents spec](https://github.com/camaraproject/QualityOnDemand/pull/224) after final review + * [#233 Alignment with changes in https://github.com/camaraproject/Template_Lead_Repository on test definitions](https://github.com/camaraproject/QualityOnDemand/pull/233) + * [#237 Single IP addresses in Device model specified with standard formats instead of patterns](https://github.com/camaraproject/QualityOnDemand/pull/237) + * PR was create to address [#230 Single IPv6 addresses within device](https://github.com/camaraproject/QualityOnDemand/issues/230) + * Jose explained the motivation, discussion and consequences of the PR + * Within `device` object only single IP addresses (IPv4 or IPv6) will be used to identify a device, the respective json formats are used to define the parameter type + * The change has only an impact for API consumers which used an IPv6 address range to identify a device (this is mentioned within the CHANGELOG.md for v0.10.0-rc) + * The schema in `applicationServer` are renamed and the restrictions of the format with regex are eliminated + * For API consumers these changes have no impact + * The PR was merged + +* PR [#228 Add GET /sessions endpoint for retrieving all active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/pull/228) + * was set back to draft, due to the fact that the discussions within the issue couldn't be concluded in time and if, would have required larger changes within the PR + * the issue and PR are postponed to the next release after v0.10.0 + +* PR [238 Creation of release candicate v0.10.0-rc](https://github.com/camaraproject/QualityOnDemand/pull/236) + * Herbert presented the PR with the updates of CHANGELOG.md, README.md and the change of version number within the YAML file to v0.10.0-rc + * The PR had already four approvals and was merged live during the meeting + * Herbert created the Github release with the tag v0.10.0-rc and the release branch release-0.10.0 + * With that the release candidate is available and all interested parties are asked to start implementation and report bugs they encounter during the implementation + * The actual release will happen most probably in January + +* Jan asked to move the user friendly links with swagger editor and redoc as first items and "hide" the link to the pure YAML file behind + * AP: Herbert will open an issue for that + + +## Discussion of Open Issues + +* [#238 Remove mobile from QoD scope](https://github.com/camaraproject/QualityOnDemand/issues/238) + * New issue created by Randy to get the scope of QoD API more inclusive beyond mobile networks + * Question if the scope is then aligned with HomeDevicesQoD or if there is an overlap + * This need to be checked and based on the result the scope can be reformulated + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Issue and related PR currently on hold until it is clarified which information about the application will be already be already part of the autorization token and can be derived from there + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * No update + * Could most probably be one option to define flows (see below) + +* [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * Potential candidate for v0.11.0 + * Adding another endpoint with `device` parameter in body of POST operation could be one option + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * Active discussion, priority candidate for v0.11.0 + * phoneNumber not allowed within query parameter => operation has to be changed to POST, with body for filter parameters + * this change will allow then to use complete `device` object to be added for filtering + +* [#51 Proposal of IpFlowDescription to allow asymmetric QoS flows and (re)introduce protocol definitions](https://github.com/camaraproject/QualityOnDemand/issues/51) + * Issue to be replaced with new issue to rework the flow definition parameters in general (devicePort, applicationServerPort) and potentially add further options, e.g. DSCP markings (see #173) + * Action Point: create new issue, close #51 + +* [#47 Include support for /PATCH sessions](https://github.com/camaraproject/QualityOnDemand/issues/47) + * "Extend duration" addressed the identified paramter for a "patch" + * Issue to be closed, new issues to be opened if other attributes of a session are to be updated + +* [#45 Need to support ability to configure fallback qos](https://github.com/camaraproject/QualityOnDemand/issues/45) + * Backlog item, currently no use case + * Might be part of upcoming QoS profiles + +* [#31 Ensure secure handling of callback URL](https://github.com/camaraproject/QualityOnDemand/issues/31) + * Call back definition are now following the CAMARA design guidelines + * Issue can most probably be closed, to be confirmed + + +## Candidate for v0.11.0 + +* Note: no merging into main for release v0.11.0 until v0.10.0 is finally released + +* Candidates for v0.11.0 (from above discussion) + * [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * New issue for flow definition rework + * will replace #51 + * will have #173 as sub issue + * Update of test definitions (.feature file) + * Discussion and update of security schema for all operations (also prerequisite for #101) + +## AOB + +* The next call will be on Friday December 15th, 14:00 CET / 13:00 GMT / 13:00 UTC diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15.md b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15.md new file mode 100644 index 0000000000000000000000000000000000000000..7e67f51d0df11aec7a9ef3863c48c8df575b80bb --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/2023/MOM-2023-12-15.md @@ -0,0 +1,111 @@ +# Camara QoD meeting - MOM-2023-12-15 + +*Friday, December 15th, 2023* + +## Attendees (probably incomplete) + +* Akos Hunyadi (Deutsche Telekom) +* Andrew Wajs (Scenera) +* Cetin Alpaycetin (Vodafone) +* Emil Zhang (Ericsson) +* Herbert Damker (Deutsche Telekom, Moderator) +* Joachim Dahlgreen (Ericsson) +* Jose Luis Urien Pinedo (Telefonica) +* Rafal Artych (Deutsche Telekom) +* Ramesh Shanmugasundaram (Spry Fox Networks) +* Randy Levensalor (CableLabs) +* Syed A Rehman (Verizon) +* Thorsten Lohmar (Ericsson) +* Toshi Wakayama (KDDI) +* ... + + +QoD minutes: [https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes](https://github.com/camaraproject/QualityOnDemand/tree/main/documentation/MeetingMinutes) + +## Agenda + +* Issues relevant for v0.10.0 (RC) +* Issues which are candidates for next release v0.11.0 +* AOB + +## Issues relevant for v0.10.0 (RC) + +* [#239 Bring user friendly links within README into top position](https://github.com/camaraproject/QualityOnDemand/issues/239) + * Fixes with PR #246 (merged during the call) + * Issue closed + +* [#238 Remove mobile from QoD scope](https://github.com/camaraproject/QualityOnDemand/issues/238) + * As long as QoD is about the access line up to the home router there is no overlap with HomeDevices QoD (see [comment](https://github.com/camaraproject/QualityOnDemand/issues/238#issuecomment-1856862249) in issue) + * Randy volunteered to prepare a PR with changes to the documentation (within YAML) and the README.md of the repository (issue assigned to him) + +* [#241 Extend the QoD API documentation with details as to what happens when qosStatus changes from available to unavailable](https://github.com/camaraproject/QualityOnDemand/issues/241) + * Agreed that this issue should be addressed within the documentation, a consistent behavior is across implementations is important + * It's useful that the session resource will exist beyond the time where the qos session became unavailable to allow API consumer who don't use/receive notifications to get the status change and reason (e.g. if polling in regular intervals) + * There will be no case where an "unavailable" QoS session will get "available" again. If we later will define such behavior (that the network tries to reestablish the requested QoS profile) we need to introduce another status (e.g. in context of issue #45, supporting fallback QoS) + * Different options discussed, about how long the session resource should be preserved after the QoS session got unavailable: + * An explicit delete by the API consumer can not be expected in all cases + * Binding to requested duration could be difficult to implement + * Emil proposed to keep the session resource for a fixed time after the session changed to unavailable + * Time to be defined, should cover at least typical polling intervals + * Emil will update his presentation with this proposal + * Design target is to allow developers to decide between notifications and polling, both methods should be sufficient to get all important information + +* [#242 Notifications](https://github.com/camaraproject/QualityOnDemand/discussions/242) + * The discussion topic is suggesting to send notifications for all changes of the status of the QoS Session resources, including the initial entering of "available" and the ones induced by API calls by the API consumer (e.g. delete of the QoS session) + * Discussed that it is important to document in which cases notifications will be send + * As far as possible within the API documentation + * In addition within the test definitions (relevant documentation for implementators) + * Sending a notification in all cases of status change is in line with the above design target, that notifications should be sufficient to get all important information + * Agreement to create an issue out of the discussion, to document the discussed behavior within the API documentation and test definitions + * ACTION POINT - Herbert to create the issue + +## Issues which are candidates for next release v0.11.0 + +These issues have the label "QoD" within https://github.com/camaraproject/QualityOnDemand/issues. +All sub project contributors are asked to add their views to the issues, so that we can start to work on the issues beginning of next year. + +* [#101 List endpoint for active sessions of authenticated user](https://github.com/camaraproject/QualityOnDemand/issues/101) + * Left over from v0.10.0 as discussion couldn't be closed, now planned for v0.11.0 + * The discussions have dependencies with #244, see below + * PR #228 on hold (draft) until the discussions are closed + * From last call: + * phoneNumber not allowed within query parameter => operation has to be changed to POST, with body for filter parameters + * this change will allow then to use complete `device` object to be added for filtering + + * [#166 Extend QoS Profile queries to list profiles based on specific users or devices](https://github.com/camaraproject/QualityOnDemand/issues/166) + * To be defined as new endpoint, POST operation with `device` object in body + * Note: identifying the device via phoneNumber might be not sufficient to return the applicable profiles, e.g. in case a device is served by multiple slices or APNs + * Further discussion within the issue + +* [#243 Rework definition of QoS flow(s)](https://github.com/camaraproject/QualityOnDemand/issues/243) + * New issue as discussed within last meeting + +* [#244 Align securitySchemes and security of QOD API spec with IdentityAndConsentManagement](https://github.com/camaraproject/QualityOnDemand/issues/244) + * New issue for v0.11.0 as discussed in last call + * Herbert proposed an additional issue to "Ensure that the QoD API does not reveal additional PII" beyond the personal information provided by the API consumer. E.g. if the device is identified by IP address, the session information should not in addition contain the phoneNumber and vice versa. Such requirement should be documented within the test definitions. Herbert to create the issue. + +* [#245 Update and enhance test definition file for QOD API](https://github.com/camaraproject/QualityOnDemand/issues/245) + * New issue as discussed within last year + + +The following two issues, labeled as "discussions" are related to the above issues: + +* [#194 Add Application Function Id (afId) or Sponsor Id](https://github.com/camaraproject/QualityOnDemand/issues/194) + * Issue and related PR currently on hold until it is clarified which information about the application will be already be already part of the autorization token and can be derived from there => #244 + +* [#173 Add support for DSCP markings for QoD sessions](https://github.com/camaraproject/QualityOnDemand/issues/173) + * Could most probably be one option to define flows => #243 + + +## v0.11.0 Release scope & timeline + +Scope of the next release v0.11.0 is described by the issues discussed above + any impacts from releases of Commonalities (v0.10.0 is in line with Commonalities v0.2.0, so any changes coming with further releases of Commonalities) +Time horizon is April/Mai 2024 (definitely after MWC Barcelona). + +## AOB + +* We will skip the call on December 29th +* The next call will be on Friday January 12th, 14:00 CET / 13:00 GMT / 13:00 UTC +* The invites for 2024 will come from the LFX Zoom platform and will be distributed via the mailing list +* For best user experience it is recommended to have an Linux Foundation account, with the same email address behind like for the mailing list subscription. An account can be created on https://openprofile.dev. The account and profile will give also access to the recordings of the meetings and to the wiki.camaraproject.org +* We will use the https://wiki.camaraproject.org for minutes going forward diff --git a/original/QualityOnDemand/documentation/MeetingMinutes/README.md b/original/QualityOnDemand/documentation/MeetingMinutes/README.md new file mode 100644 index 0000000000000000000000000000000000000000..4ed7ba0158907237a08b0a644f0246c235e73c0c --- /dev/null +++ b/original/QualityOnDemand/documentation/MeetingMinutes/README.md @@ -0,0 +1,5 @@ +## Meeting Minutes of Quality on Demand Sub Project + +Starting with the beginning of 2024 the meeting minutes of Quality on Demand calls are within the CAMARA Wiki at https://lf-camaraproject.atlassian.net/wiki/x/ABje. + +Meeting minutes of 2023 and before are here in the repository. diff --git a/original/RainfallIntensity/README.md b/original/RainfallIntensity/README.md new file mode 100644 index 0000000000000000000000000000000000000000..c29fb5dde9c3083c95df7fa1b7f8c2132d668b60 --- /dev/null +++ b/original/RainfallIntensity/README.md @@ -0,0 +1,45 @@ + + + + + + + + + +# RainfallIntensity + +Sandbox API Repository to describe, develop, document, and test the RainfallIntensity Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/DYDEH) + +## Scope + +* Service API(s) “RainfallIntensity” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Obtain the power measurements for the communication links inside a geographical area for a specific time period. The data includes the time of measurement, the transmit and received power, and the link ID (which identifies each link uniquely). + * Obtain the metadata of the communication links within a geographical area. The metadata includes the link ID, time of update, signal frequecny, signal polarization (horizontal or vertical), and location (latetude and longitude) of the transmitter and the receiver. + * Obtain the rainfall data associated with communciation links inside a geographical are for a specific time. The rainfall data include the estimation of rainfall, time stamp, and link ID. +* Describe, develop, document, and test the API(s) +* Started: January 2026 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/AgDHH) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/RainfallIntensity/code/API_definitions/README.MD b/original/RainfallIntensity/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/RainfallIntensity/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/RainfallIntensity/documentation/API_documentation/README.MD b/original/RainfallIntensity/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/RainfallIntensity/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/RainfallIntensity/documentation/SupportingDocuments/README.MD b/original/RainfallIntensity/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/RainfallIntensity/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/RegionDeviceCount/README.md b/original/RegionDeviceCount/README.md new file mode 100644 index 0000000000000000000000000000000000000000..457790e9f469e950c9cd8638a12eab2926fcb744 --- /dev/null +++ b/original/RegionDeviceCount/README.md @@ -0,0 +1,52 @@ + + + + + + + + + +# RegionDeviceCount + +Sandbox API Repository to describe, develop, document, and test the RegionDeviceCount Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/JSTe) + +## Scope +* Service APIs for “RegionDeviceCount” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points.In addition, this API also provides a filtering function. Customers can filter devices by passing in different constraints. Currently, it supports two filtering conditions: roaming status and device type, and it is designed to be extended in the future + * NOTE: The scope of this API should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/RegionDeviceCount/releases/tag/r2.2) (Fall25), with the following API versions: + * **region-device-count v0.2.0** + [[YAML]](https://github.com/camaraproject/RegionDeviceCount/blob/r2.2/code/API_definitions/region-device-count.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/r2.2/code/API_definitions/region-device-count.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/r2.2/code/API_definitions/region-device-count.yaml) +* The latest public release is always available here: https://github.com/camaraproject/RegionDeviceCount/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/RegionDeviceCount/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/RegionDeviceCount/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-Weekly on Fridays 11:00 CET/CEST / 09:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/91734372257?password=28df8c0a-941a-4f41-adc2-fd5de2791a96) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/RegionDeviceCount) +* Mailing List + + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/RegionDeviceCount/code/API_definitions/region-device-count.yaml b/original/RegionDeviceCount/code/API_definitions/region-device-count.yaml new file mode 100644 index 0000000000000000000000000000000000000000..c09e2b1059a5d29fdd55a2f6440bc717abc84031 --- /dev/null +++ b/original/RegionDeviceCount/code/API_definitions/region-device-count.yaml @@ -0,0 +1,750 @@ +openapi: 3.0.3 +info: + title: Region Device Count + description: >- + Region Device Count API enables API consumers to obtain the number of devices within a certain geographical area during a specific time interval. + + # Introduction + + This API allows for the API Consumer to query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points. + This functionality can be used for multiple use cases, some of the possible use cases for this API are: + + - [Emergency Rescue](https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/main/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md) + + - [Outdoor Live Streaming](https://raw.githubusercontent.com/camaraproject/RegionDeviceCount/main/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md) + + # Relevant terms and definitions + + * **Device Count**: Refers to the total number of devices that appear within a given area and a specific time interval. A device will be counted as long as it appears at least once in the specified area during the time interval. + + * **Notification URL and token**: Developers may provide a callback URL (`sink`) for receiving an async response. This is an optional parameter. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + # API Functionality + + ## Request Parameters and Area Definition + + When making a request, the API consumer needs to specify the area, start time, end time, and filter conditions in the request body. The area can be defined as a circle or a polygon. For a circular area, the center and radius must be provided; for a polygon area, a list of longitude and latitude points must be provided. If the start and end times are not provided, the API will return the current number of devices in the area. + + ## Filter Condition Application + + The filter condition is used for precise device filtering and currently includes two filtering criteria: `roamingStatus` and `deviceType`, with support for future expansion. The `IN` logic is applied for multiple filter items within a single filtering criterion, and the `AND` logic is used between multiple filtering criteria. + + + For example, "filter":{"roamingStatus": ["roaming"],"deviceType": ["human device","IoT device"]}" means the API will only return the number of human network devices and IoT devices in roaming mode. "filter":{"roamingStatus": ["non-roaming"]}" will return the number of all non-roaming devices. Note that at least one filtering criterion must be provided; otherwise, the request will be invalid. + + ## Response Result Explanation + + The API response returns a RegionDeviceCountResponse object containing the device count and status. The status values include `SUPPORTED_AREA` (the entire requested area is supported, and the device count for the entire area is returned, with 100% telecom coverage), `PART_OF_AREA_NOT_SUPPORTED` (part of the area is outside the telecom operator's coverage area, and only the device count within the coverage area is returned, with 50% <= telecom coverage < 100%), `AREA_NOT_SUPPORTED` (the entire requested area has no telecom coverage, and no data is returned, with telecom coverage < 50%), `DENSITY_BELOW_PRIVACY_THRESHOLD` (the number of connected devices in the area is below the local regulatory privacy threshold), and `TIME_INTERVAL_NO_DATA_FOUND` (no device count data is found within the requested time interval). + + ## Callback Function + + The standard behaviour of the API is synchronous, although for large area requests the API may behave asynchronously. An API invoker can enforce asynchronous behaviour by providing a callback URL (`sink`) + is in the request, in this case the API sends a callback to the callback URL provided with the result of the request. If `sink` is included, it is RECOMMENDED for the client to provide as well the `sinkCredential` property to protect the notification endpoint. In the current version,`sinkCredential.credentialType` MUST be set to `ACCESSTOKEN` if provided. + + For requests with a combination of area, startTime and endTime properties involving an amount of processing that cannot be processed synchronously, the API returns the error response REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE. + + For requests with a combination of area, startTime and endTime properties too big for both synchronous and asynchronous processing, the API returns the error response REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST. + + + # Authorization and Authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + Region Device Count API does not involve the input and output of user personal data.Therefore, the access to Region Device Count APII is defined as `Client Credentials - 2-legged`. Please refer to [Identify and Consent Management](https://github.com/camaraproject/IdentityAndConsentManagement/) for the latest detailed specification of this authentication/authorization flow. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/RegionDeviceCount +servers: + - url: '{apiRoot}/region-device-count/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Region Device Count + description: This API allows for the API Consumer to query device count in the specified area during a certain time interval.The query area can be a circle or a polygon composed of longitude and latitude points. +paths: + /count: + post: + tags: + - Region Device Count + summary: API operation to get the device count in the specified area during a certain time interval. + description: | + Get the number of devices in the specified area during a certain time interval. + - The query area can be a circle or a polygon composed of longitude and latitude points. + - If the areaType is circle, the circleCenter and circleRadius must be provided; if the area is a polygon, the point list must be provided. + - If starttime and endtime are not passed in,this api should return the current number of devices in the area. + - If the device appears in the specified area at least once during the certain time interval, it should be counted. + + operationId: count + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountRequestBody' + examples: + LOCATION_CIRCLE: + $ref: "#/components/examples/RETRIEVAL_CIRCLE" + LOCATION_POLYGON: + $ref: "#/components/examples/RETRIEVAL_POLYGON" + required: true + callbacks: + regionDeviceCountCallback: + '{$request.body#/sink}': + post: + tags: + - Region Device Count + summary: 'Region Device Count Callback' + description: | + Important: this endpoint is to be implemented by the API consumer. + The Region Device Count server will call this endpoint when the request result is ready. + operationId: postRegionDeviceCountNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: Region device count result. + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountResponse' + examples: + SUPPORTED_AREA: + $ref: "#/components/examples/SUPPORTED_AREA" + PART_OF_AREA_NOT_SUPPORTED: + $ref: "#/components/examples/PART_OF_AREA_NOT_SUPPORTED" + AREA_NOT_SUPPORTED: + $ref: "#/components/examples/AREA_NOT_SUPPORTED" + DENSITY_BELOW_PRIVACY_THRESHOLD: + $ref: "#/components/examples/DENSITY_BELOW_PRIVACY_THRESHOLD" + responses: + '204': + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '410': + $ref: '#/components/responses/Generic410' + security: + - {} + - notificationsBearerAuth: [] + responses: + '200': + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegionDeviceCountResponse' + examples: + SUPPORTED_AREA: + $ref: "#/components/examples/SUPPORTED_AREA" + PART_OF_AREA_NOT_SUPPORTED: + $ref: "#/components/examples/PART_OF_AREA_NOT_SUPPORTED" + AREA_NOT_SUPPORTED: + $ref: "#/components/examples/AREA_NOT_SUPPORTED" + DENSITY_BELOW_PRIVACY_THRESHOLD: + $ref: "#/components/examples/DENSITY_BELOW_PRIVACY_THRESHOLD" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '429': + $ref: '#/components/responses/Generic429' + security: + - openId: + - region-device-count:count +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for cross-service tracking + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + RegionDeviceCountRequestBody: + type: object + description: Payload to get the count of devices in the specific region. + properties: + area: + $ref: "#/components/schemas/Area" + starttime: + type: string + format: date-time + description: Starting timestamp for counting the number of devices in the area. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + endtime: + type: string + format: date-time + description: Ending timestamp for counting the number of devices in the area. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-04T14:27:08.312+02:00" + filter: + $ref: "#/components/schemas/Filter" + sink: + type: string + format: uri + description: The URL where the API response will be asynchronously delivered, using the HTTP protocol. + example: 'https://endpoint.example.com/sink' + sinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + allOf: + - $ref: '#/components/schemas/SinkCredential' + Area: + type: object + properties: + areaType: + $ref: "#/components/schemas/AreaType" + required: + - areaType + discriminator: + propertyName: areaType + mapping: + CIRCLE: "#/components/schemas/Circle" + POLYGON: "#/components/schemas/Polygon" + AreaType: + type: string + description: | + Type of this area. + CIRCLE - The area is defined as a circle. + POLYGON - The area is defined as a polygon. + enum: + - CIRCLE + - POLYGON + + Circle: + description: Circular area + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - center + - radius + properties: + center: + $ref: "#/components/schemas/Point" + radius: + type: number + description: Distance from the center in meters + minimum: 1 + + Polygon: + allOf: + - $ref: "#/components/schemas/Area" + - type: object + required: + - boundary + properties: + boundary: + $ref: "#/components/schemas/PointList" + + PointList: + type: array + items: + $ref: "#/components/schemas/Point" + minItems: 3 + maxItems: 15 + + Point: + type: object + description: Coordinates (latitude, longitude) defining a location in a map + required: + - latitude + - longitude + properties: + latitude: + $ref: "#/components/schemas/Latitude" + longitude: + $ref: "#/components/schemas/Longitude" + example: + latitude: 50.735851 + longitude: 7.10066 + + Latitude: + description: Latitude component of a location + type: number + format: double + minimum: -90 + maximum: 90 + + Longitude: + description: Longitude component of location + type: number + format: double + minimum: -180 + maximum: 180 + Filter: + description: | + This parameter is used to filter devices. Currently, two filtering criteria are defined, `roamingStatus` and `deviceType`, which can be expanded in the future. `IN` logic is used used for multiple filtering items within a single filtering criterion, `AND` logic is used between multiple filtering criteria. + - If a filtering critera is not provided, it means that there is no need to filter this item. + - At least one of the criteria must be provided,a filter without any criteria is not allowed. + - If no filtering is required, this parameter does not need to be provided. + For example ,`"filter":{"roamingStatus": ["roaming"],"deviceType": ["human device","IoT device"]}` means the API need to return the count of human network devices and IoT devices that are in roaming mode.`"filter":{"roamingStatus": ["non-roaming"]}` means that the API need to return the count of all devices that are not in roaming mode. + type: object + properties: + roamingStatus: + description: Filter whether the device is in roaming mode,'roaming' represents the need to filter devices that are in roaming mode,'non-roaming' represents the need to filter devices that are not roaming. + type: array + items: + type: string + enum: + - 'roaming' + - 'non-roaming' + minItems: 1 + deviceType: + description: Filtering by device type, 'human device' represents the need to filter for human network devices, 'IoT device' represents the need to filter for IoT devices, and 'other' represents the need to filter for other types of devices. + type: array + items: + type: string + enum: + - 'human device' + - 'IoT device' + - 'other' + minItems: 1 + anyOf: + - required: ['roamingStatus'] + - required: ['deviceType'] + SinkCredential: + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: '#/components/schemas/PlainCredential' + ACCESSTOKEN: '#/components/schemas/AccessTokenCredential' + REFRESHTOKEN: '#/components/schemas/RefreshTokenCredential' + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). For the current version of the API the type MUST be set to `Bearer`. + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: '#/components/schemas/SinkCredential' + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + RegionDeviceCountResponse: + type: object + description: RegionDeviceCount result + properties: + count: + $ref: '#/components/schemas/Count' + status: + $ref: '#/components/schemas/Status' + Count: + description: Device Count + type: number + Status: + description: | + SUPPORTED_AREA: The whole requested area is supported Region Device Count for the entire requested area is returned - Telco Coverage = 100 % + + PART_OF_AREA_NOT_SUPPORTED: Part of the requested area is outside the MNOs coverage area, the area outside the coverage area are not returned - 100% >Telco Coverage >=50% + + AREA_NOT_SUPPORTED: The whole requested area is outside the MNO coverage area No data will be returned- Telco Coverage <50% + + DENSITY_BELOW_PRIVACY_THRESHOLD: The number of connected devices is below privacy threshold of local regulation + + TIME_INTERVAL_NO_DATA_FOUND: Unable to find device count data within the requested time interval + type: string + enum: + - SUPPORTED_AREA + - PART_OF_AREA_NOT_SUPPORTED + - AREA_NOT_SUPPORTED + - DENSITY_BELOW_PRIVACY_THRESHOLD + - TIME_INTERVAL_NO_DATA_FOUND + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - REGION_DEVICE_COUNT.TIME_INVALID_ARGUMENT + - REGION_DEVICE_COUNT.INVALID_END_DATE + - REGION_DEVICE_COUNT.INVALID_CIRCLE_AREA + - REGION_DEVICE_COUNT.INVALID_POLYGON_AREA + - INVALID_CREDENTIAL + - INVALID_TOKEN + - REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE + - REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument, request body or query param." + GENERIC_400_TIME_INTERVAL_NOT_SATISFIABLE: + value: + status: 400 + code: REGION_DEVICE_COUNT.TIME_INVALID_ARGUMENT + message: "starttime and endtime cannot be passed separately. Either both are passed or neither is passed." + GENERIC_400_INVALID_END_DATE: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_END_DATE + message: "Indicated endTime is earlier than the startTime." + GENERIC_400_INVALID_CIRCLE_AREA: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_CIRCLE_AREA + message: "Missing circle center or radius." + GENERIC_400_INVALID_POLYGON_AREA: + value: + status: 400 + code: REGION_DEVICE_COUNT.INVALID_POLYGON_AREA + message: "The area is not a polygon shape or has an arbitrary complexity." + GENERIC_400_INVALID_CREDENTIAL: + value: + status: 400 + code: INVALID_CREDENTIAL + message: "Only Access token is supported" + GENERIC_400_INVALID_TOKEN: + value: + status: 400 + code: INVALID_TOKEN + message: "Only bearer token is supported" + GENERIC_400_UNSUPPORTED_SYNC_RESPONSE: + value: + status: 400 + code: REGION_DEVICE_COUNT.UNSUPPORTED_SYNC_RESPONSE + message: "Indicated combination of area or time interval is too big for a sync response" + GENERIC_400_UNSUPPORTED_REQUEST: + value: + status: 400 + code: REGION_DEVICE_COUNT.UNSUPPPORTED_REQUEST + message: "Indicated combination of area or time interval is too big" + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic429: + description: Either out of resource quota or reaching rate limiting + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + RETRIEVAL_CIRCLE: + value: + area: + areaType: CIRCLE + center: + latitude: 45.754114 + longitude: 4.860374 + radius: 800 + starttime: "2023-07-03T14:27:08.312+02:00" + endtime: "2023-07-04T14:27:08.312+02:00" + filter: + roamingStatus: ["roaming"] + deviceType: ["human device", "IoT device"] + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + RETRIEVAL_POLYGON: + value: + area: + areaType: POLYGON + boundary: + - latitude: 45.754114 + longitude: 4.860374 + - latitude: 45.753845 + longitude: 4.863185 + - latitude: 45.753916 + longitude: 4.866531 + - latitude: 45.754116 + longitude: 4.876353 + starttime: "2023-07-03T14:27:08.312+02:00" + endtime: "2023-07-04T14:27:08.312+02:00" + filter: + roamingStatus: ["non-roaming"] + deviceType: ["other"] + sink: "https://endpoint.example.com/sink" + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + SUPPORTED_AREA: + value: + count: 100 + status: SUPPORTED_AREA + PART_OF_AREA_NOT_SUPPORTED: + value: + count: 100 + status: PART_OF_AREA_NOT_SUPPORTED + AREA_NOT_SUPPORTED: + value: + status: AREA_NOT_SUPPORTED + DENSITY_BELOW_PRIVACY_THRESHOLD: + value: + status: DENSITY_BELOW_PRIVACY_THRESHOLD diff --git a/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md b/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md new file mode 100644 index 0000000000000000000000000000000000000000..61531bbbd3027a65dd7518adf93646a8ab2d8e23 --- /dev/null +++ b/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md @@ -0,0 +1,10 @@ +# RegionDeviceCount API User Story - Emergency Rescue + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an emergency rescue worker, I hope to be able to obtain the number of users in an area where a special emergency activities could be needed through an API, so as to quickly understand the situation, plan and guide the rescue work..Here is my requirements.
                                                                  •I hope to obtain the number of connected devices on people in the area by providing coordinates or boundary information.
                                                                  •I need the information returned by the API to include the total number and distribution of the devices in that area.
                                                                  •I need to obtain real-time information| +| ***Roles, Actors and Scope*** | **Roles:** API Customer: emergency rescue worker.
                                                                  API Provider:Communication Service Provider (CSP).
                                                                  **Scope:** Returns the real-time number of devices in a specific area through an API | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                  1. The Customer has been onboarded to the CSP's API platform.
                                                                  2. The Customer has successfully subscribed to the RegionDeviceCount product from the product catalog.
                                                                  3. The means to get the access token are known to the API Customer to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** API Customer initiate requests to query the number of devices in a certain area
                                                                    **Ends when:** CSP returns the number of devices in the area to the API Customer. | +| ***Post-conditions*** | CSP returns accurate statistical results, and emergency rescue worker.can quickly locate key rescue areas based on results.| +| ***Exceptions*** | Several exceptions might occur during the RegionDeviceCount API operations
                                                                    - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                    - Invalid input: Not valid input data to invoke operation (e.g.Area format error, or inability to obtain valid data within the area).
                                                                    | diff --git a/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md b/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md new file mode 100644 index 0000000000000000000000000000000000000000..6491862958cc7ff58ae33542a6b09517d5b1cfbd --- /dev/null +++ b/original/RegionDeviceCount/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md @@ -0,0 +1,10 @@ +# RegionDeviceCount API User Story - Outdoor Live Streaming + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an outdoor anchor and plan to conduct outdoor live streaming activities in different regions. In order to estimate the possible number of viewers and effectively choose a live streaming location, I need to understand the potential number of viewers in different area.Here is my requirements.
                                                                    • I hope to obtain the number of users in a specific area through an API, so that I can choose locations with high audience potential for live streaming based on this data.
                                                                    • I need an API that can provide information on the activity level of users in the area, in order to determine the activity time of users in that area and arrange the best live broadcast time.
                                                                    • I hope the response time of the API is fast, so that decisions can be made quickly before planning and actual live broadcasts.| +| ***Roles, Actors and Scope*** | **Roles:** End User:Outdoor anchor
                                                                    API Customer: Live Streaming Application.
                                                                    API Provider:Communication Service Provider (CSP).
                                                                    **Scope:** Returns the number of users in a specific area during a certain time interval through an API | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                    1. The Customer has been onboarded to the CSP's API platform.
                                                                    2. The Customer has successfully subscribed to the RegionDeviceCount product from the product catalog.
                                                                    3. The outdoor anchor has been onboarded to the live streaming application.
                                                                    4. The means to get the access token are known to the API Customer to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** Outdoor anchors initiate requests through live streaming application to query the number of devices in a certain area at a certain time interval
                                                                      **Ends when:** CSP returns the number of devices in the area to the live streaming app, and the live streaming app presents the results to the anchors. | +| ***Post-conditions*** | CSP returns accurate statistical results, and users can choose suitable live streaming areas based on the query results | +| ***Exceptions*** | Several exceptions might occur during the RegionDeviceCount API operations
                                                                      - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                      - Invalid input: Not valid input data to invoke operation (e.g.Area format error, or inability to obtain valid data within the area).
                                                                      | diff --git a/original/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist.md b/original/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..6f781541320191361bc7e4b2e93d6fbddb30dbab --- /dev/null +++ b/original/RegionDeviceCount/documentation/API_documentation/region-device-count-API-Readiness-Checklist.md @@ -0,0 +1,20 @@ +# API Readiness Checklist + +Checklist for region-device-count v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                      public | stable
                                                                      public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/region-device-count.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.2.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/region-device-count.yaml) | +| 6 | User stories | O | O | O | M | Y | [UserStory1-Emergency_Rescue](/documentation/API_documentation/RDC_User_Story_Emergency_Rescue.md) [UserStory2-Outdoor_Live_Streaming](/documentation/API_documentation/RDC_User_Story_Outdoor_Live_Streaming.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/region-device-count.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/region-device-count.feature) | +| 9 | Test result statement | O | O | O | M | N | To be provided | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81134323/RegionDeviceCount+API+description ) | + diff --git a/original/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10.md b/original/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10.md new file mode 100644 index 0000000000000000000000000000000000000000..35a064ec6effa691790692fc347868b99b663e17 --- /dev/null +++ b/original/RegionDeviceCount/documentation/MeetingMinutes/MOM-2024-05-10.md @@ -0,0 +1,38 @@ +# CAMARA Network Slice Booking Meeting - MOM-2024-05-10 + +*Friday, May 10th, 2024* + +## Attendees (probably incomplete) +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* Ludovic Robert (Orange) + +## Agenda +* Welcome new contributors. +* Issues relevant for v0.1.0 +* AOB + +## Issues relevant for v0.1.0 +* Meeting Schedule Adjust + * Meeting Links are adjusted. Including meeting links. Links of S2C, Region User Count, Network Slice API are split into 3 different meeting links as suggested. + * Meeting times are adjusted. Later the Bi-weekly meeting will start from 5pm CST, 11am CEST. +* Issue#12 Add license file to repository + * Shuting Qing will add the license file. +* Issue#10 User Story 1 - Emergency Rescue,Issue#11 User Story 2 - Outdoor Live Streaming + * Continue the discussion. If there are no other comments, they will be placed in markup format under the documentation folder of the project. +* Issue#9 Support for scenarios when API cannot return a devices count is needed + * Add a status parameter to yaml to identify the query status, with the following enumeration values + * SUBORTED-AREA: The whole request area is supported Population density data for the entire requested area is returned + * Part of the requested area is outside the MNOs coverage area, the cells outside the coverage area are not returned + * AREA-NOT-SUPPORTED: The whole requested area is outside the MNO coverage area No data will be returned + * DENSITY-BELOW-PRIVACY THRESHOLD: The number of connected devices is below privacy threshold of local regulation + * Some specific definitions still need further discussion and clarification +* Issue#8 Support for scenarios when API cannot return a devices count is needed + * The meeting decided to change the API name to RegionDeviceCount to better align with the API intent. Ludovic will help inquire with the working group about the specific process. + +## v0.1.0 Release scope & timeline +* Need to follow up with CAMARA release management. + +## AOB +1. The next call will be on Friday, May 24th, 17:00 CST / 11:00 CEST diff --git a/original/RegionDeviceCount/documentation/MeetingMinutes/README.MD b/original/RegionDeviceCount/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/RegionDeviceCount/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom.md b/original/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom.md new file mode 100644 index 0000000000000000000000000000000000000000..9f216fd8c879290d994d92a817958ee9a7936823 --- /dev/null +++ b/original/RegionDeviceCount/documentation/SupportingDocuments/APIproposal_RegionDeviceCount_ChinaUnicom.md @@ -0,0 +1,13 @@ +| **Field** | Description | +| ---- | ----- | +| API family name | Region Device Count | +| API family owner | China Unicom | +| Initial API Contributors | Fan Yang - China Unicom , Jin Xu - Huawei | +| API summary | **Description**
                                                                      This API allows for the API Consumer to query the number of active users (i.e., excluding idle mode users). lin the specified area. The query area can be a circle or a polygon composed of longitude and latitude points.
                                                                      **Use Cases**
                                                                      User Story 1 : Emergency Rescue
                                                                      - As an emergency rescue worker, I hope to be able to obtain the number of users in an area where a special emergency activities could be needed through an API, so as to quickly understand the situation, plan and guide the rescue work.
                                                                      | +| Technical viability | This API is based on real-time location information expansion. It allows obtaining, on a per operator basis, the number of active users in a certain area based on their real-time location. | +| Commercial viability | For use in emergency rescue, disaster relief, intelligent transportation, smart tourism and other scenarios| +| YAML code available? | NO
                                                                      To be provided | +| Validated in lab/productive environments? | YES
                                                                      Available in China UniCom test environment | +| Validated with real customers? | YES
                                                                      For emergency rescue use by the Blue Eye Emergency Rescue Platform | +| Validated with operators? | YES
                                                                      Available for China Unicom in China | +| Supporters in API Backlog Working Group | China Unicom,Huawei | diff --git a/original/SessionInsights/README.md b/original/SessionInsights/README.md new file mode 100644 index 0000000000000000000000000000000000000000..3b4c41bddbd8f10b31900680d82a0e8170ee3665 --- /dev/null +++ b/original/SessionInsights/README.md @@ -0,0 +1,44 @@ + + + + + + + + + +# SessionInsights + +Sandbox API Repository to describe, develop, document, and test the SessionInsights Service API(s) in group with [Connectivity Insights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/93946006/Connectivity+Insights) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/44CaBQ) + +## Scope + +* Concept and Service APIs for “SessionInsights” (see APIBacklog.md) +* The API provides an API Consumer with the ability to: + - report application KPIs to network operator + - receive score from network operator + - receive root cause analysis and recommended corrective actions + - request service improvements +* Note: in first steps the concept will be described with user stories. The relation to existing APIs (e.g. application-profiles, connectivity-insights, quality-on-demand) will be describe to identify if any and which new API(s) are needed +* Describe the concept, develop, document, and test the APIs +* Started: September 2024 +* Originally proposed as Quality by Design (QbD) - has been renamed to SessionInsights to better reflect the scope of the API + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing +* Meetings are held virtually + * Schedule: Bi-weekly on Wednesday at 8AM PST (see https://wiki.camaraproject.org/display/CAM/ConnectivityInsights) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/92345695827?password=35dff2b2-058d-44de-bd7e-67d08c9e9f9d) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/vzve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-coi. + * A message to the community of this Sub Project can be sent using sp-coi@lists.camaraproject.org. diff --git a/original/SessionInsights/code/API_definitions/README.MD b/original/SessionInsights/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/SessionInsights/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/SessionInsights/code/API_definitions/session-insights.yaml b/original/SessionInsights/code/API_definitions/session-insights.yaml new file mode 100644 index 0000000000000000000000000000000000000000..1460840df19478308b4bbc40fdbe49548d4ca2d7 --- /dev/null +++ b/original/SessionInsights/code/API_definitions/session-insights.yaml @@ -0,0 +1,1059 @@ +openapi: 3.0.3 +info: + title: Session Insights + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + description: | + The Session Insights API is part of the CAMARA Connectivity Insights API group. It extends the capabilities of the Connectivity Insights API by enabling applications to continuously monitor and evaluate their real-time session quality, based on observed KPIs and network operator feedback. + + While the Connectivity Insights API allows applications to query whether a network can meet predefined performance thresholds (e.g., jitter, packet loss, bitrate), the Session Insights API supports the lifecycle of an ongoing session. It allows applications to stream KPI metrics to the network operator, receive dynamic scoring on current session performance, and engage in adaptive optimization strategies. + + # Key Features + + - Create a monitoring session using an existing Application Profile. + - Send application-level KPIs (e.g., latency, jitter, throughput, loss) to the network operator. + - Receive a Session Insights Score reflecting network-evaluated session quality. + - Respond to events and adjust application configuration. + - Receive notifications and root cause analysis (RCA) when session quality degrades. + - Request network service improvements using complementary CAMARA APIs (e.g., QualityOnDemand, NetworkAccessManagement). + - Gracefully terminate the session when monitoring is no longer needed. + + # Use of Application Profiles API + + This API leverages CAMARA’s [Application Profiles](https://github.com/camaraproject/ApplicationProfiles) to define threshold criteria for session quality. The Application Profile specifies the application's expected network performance requirements and is referenced when creating a session. + + # Example Use Cases + + ## Wi-Fi Congestion Mitigation + - Application sets thresholds for latency and packet loss. + - Session score drops due to congestion, triggering an RCA event. + - RCA identifies local Wi-Fi congestion; application adjusts QoS policies (e.g., enables WMM) to prioritize traffic. + + ## Access Network Impairment + - Degraded score attributed to poor signal or congestion in the access network. + - Application requests service enhancement through APIs like QualityOnDemand or NetworkAccessManagement. + + # Authorization and Authentication + + ## Identifying the [ device | phone number ](*) from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` object is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same [ device | phone number ](*) is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/SessionInsights + +servers: + - url: "{apiRoot}/session-insights/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: | + API root, defined by service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Session Insights + description: | + Manage the lifecycle of real-time monitoring sessions between an application and the network. + Applications can stream KPIs, receive session scores and event notifications, and take actions + based on current session quality and network conditions. + + +paths: + /sessions: + post: + tags: + - Session Insights + summary: Create a Session Insights session + description: | + Create a new session for monitoring application performance and network + quality. The session can be used to stream KPIs, receive session + scores, and handle RCA events. + + The session is created under an existing Application Profile, which + defines the expected performance thresholds and other parameters. + + The operator allocates a sink (HTTP webhook or MQTT topic) for the + application to send metrics and receive notifications. + operationId: createSession + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + oneOf: + - $ref: "#/components/schemas/HTTPSessionRequest" + - $ref: "#/components/schemas/MQTTSessionRequest" + discriminator: + propertyName: protocol + responses: + "201": + description: Session created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSessionResponse" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "409": + $ref: "#/components/responses/Conflict409" + "422": + $ref: "#/components/responses/Generic422" + + /sessions/{sessionId}: + get: + tags: + - Session Insights + summary: "Get session by sessionId" + description: | + Retrieve the details of a specific session by its operator-assigned + session ID. + operationId: getSession + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: Session detail + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Session" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + + delete: + tags: + - Session Insights + summary: Delete session + description: | + Delete a session by its operator-assigned session ID. This will stop + all notifications and metrics streaming for the session. + operationId: deleteSession + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + + /retrieve-sessions: + post: + tags: + - Session Insights + summary: Retrieve Session Insights sessions by device + description: | + Retrieve all Session Insights sessions for a given device. + + **Notes:** + - This operation allows retrieving all active or historical sessions associated with a device. + - It uses POST instead of GET to allow passing sensitive device identifiers in the body, per CAMARA guidelines. + - The request must include a `device` object if using a two-legged token. If using a three-legged token, do not provide a `device` as the device is derived from the token. + + operationId: retrieveSessionsByDevice + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + description: Parameters to get Session Insights session information by device + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsInput" + required: true + responses: + "200": + description: An array of sessions matching the specified device. Empty array if none found. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/RetrieveSessionsOutput" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + /sessions/{sessionId}/metrics: + post: + tags: + - Session Insights + summary: Send session metrics + description: | + Stream application-level KPIs (e.g., latency, jitter, throughput, loss) + to the network operator for the specified session. This is used to + evaluate session quality and trigger notifications if thresholds are + breached. + operationId: sendSessionMetrics + parameters: + - name: sessionId + in: path + description: Operator-assigned session ID + required: true + schema: + $ref: "#/components/schemas/SessionId" + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/MetricsPayload" + responses: + "204": + description: Metrics accepted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/BadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Forbidden403" + "404": + $ref: "#/components/responses/NotFound404" + "410": + $ref: "#/components/responses/Generic410" + "422": + $ref: "#/components/responses/Generic422" + +components: + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + SessionId: + description: Session ID in UUID format + type: string + format: uuid + + SessionRequest: + description: | + Request body for creating a new session. The session is created under + an existing Application Profile, which defines the expected + performance thresholds and other parameters. + + The operator allocates a sink (HTTP webhook or MQTT topic) for the + application to send metrics and receive notifications. + type: object + properties: + applicationProfileId: + $ref: "#/components/schemas/ApplicationProfileId" + device: + $ref: "#/components/schemas/Device" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + applicationSessionId: + type: string + description: | + Optional app-level meeting / match / stream ID used for correlation. + example: "meet-12345" + protocol: + $ref: "#/components/schemas/Protocol" + types: + type: array + items: + $ref: "#/components/schemas/EventType" + required: + - applicationProfileId + - device + - applicationServer + - protocol + - subscribedEventTypes + + SessionBase: + type: object + properties: + id: + type: string + description: Operator-assigned session ID + example: "op-sess-abc123" + applicationSessionId: + type: string + description: Application-provided session reference + example: "meet-12345" + device: + $ref: "#/components/schemas/DeviceResponse" + applicationServer: + $ref: "#/components/schemas/ApplicationServer" + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + description: | + • HTTP → webhook URL (from request) + • MQTT → quality topic (allocated by operator) + subscribedEventTypes: + type: array + items: + $ref: "#/components/schemas/EventType" + startTime: + type: string + format: date-time + expiresAt: + type: string + format: date-time + required: + - id + - device + - applicationServer + - protocol + - sink + - subscribedEventTypes + - startTime + + HTTPSettings: + type: object + description: No additional settings + + MQTTSettings: + type: object + required: [brokerUri, metricsTopic, qualityTopic, qos] + properties: + brokerUri: + type: string + format: uri + metricsTopic: + type: string + description: Topic the **application PUBLISHES** KPI messages to + example: session/op-sess-abc123/appSession/meet-12345/metrics + qualityTopic: + type: string + description: Topic the **application SUBSCRIBES** to for CloudEvents + example: session/op-sess-abc123/appSession/meet-12345/quality + qos: + type: integer + enum: + - 0 + - 1 + retain: + type: boolean + default: false + messageExpiryInterval: + type: integer + + HTTPSessionRequest: + allOf: + - $ref: "#/components/schemas/SessionRequest" + - type: object + properties: + sink: + type: string + description: Webhook URL for event delivery + sinkCredential: + type: string + description: Optional credential for HTTP callbacks + required: + - sink + + MQTTSessionRequest: + allOf: + - $ref: "#/components/schemas/SessionRequest" + - type: object + properties: + sinkCredential: + type: string + description: Credential for MQTT broker access + + HTTPSession: + allOf: + - $ref: "#/components/schemas/SessionBase" + - type: object + properties: + protocol: + type: string + enum: + - "HTTP" + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + MQTTSession: + allOf: + - $ref: "#/components/schemas/SessionBase" + - type: object + properties: + protocol: + type: string + enum: + - "MQTT3" + - "MQTT5" + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + Session: + oneOf: + - $ref: "#/components/schemas/HTTPSession" + - $ref: "#/components/schemas/MQTTSession" + discriminator: + propertyName: protocol + + CreateHTTPSession: + allOf: + - $ref: "#/components/schemas/HTTPSession" + - type: object + properties: + sinkCredential: + type: string + description: Returned only on creation (HTTP) + + CreateMQTTSession: + allOf: + - $ref: "#/components/schemas/MQTTSession" + - type: object + properties: + sinkCredential: + type: string + description: Broker credential (creation only) + + CreateSessionResponse: + oneOf: + - $ref: "#/components/schemas/CreateHTTPSession" + - $ref: "#/components/schemas/CreateMQTTSession" + discriminator: + propertyName: protocol + + Device: + description: | + End-user equipment able to connect to a network. Examples of + devices include smartphones or IoT sensors/actuators. + + The developer can choose to provide the below specified device + identifiers: + + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their + request, the API provider must return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do + not match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers with a + given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In + 3GPP terminology, it corresponds to the GPSI formatted with the + External Identifier ({Local Identifier}@{Domain Identifier}). Unlike + the telephone number, the network access identifier is not subjected + to portability ruling in force, and is individually managed by each + operator. + type: string + example: "123456789@domain.com" + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile + networks it corresponds to the MSISDN (Mobile Station International + Subscriber Directory Number). In order to be globally unique it has to + be formatted in international format, according to E.164 standard, + optionally prefixed with '+'. + type: string + pattern: '^\+?[0-9]{5,15}$' + example: "123456789" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is + not in use) then the same address should be specified for both + publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its + publicAddress and publicPort, or separately by its allocated IPv6 + address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: {"publicAddress": "84.125.93.10", "publicPort": 59765} + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + + The session shall apply to all IP flows between the device subnet and + the specified application server, unless further restricted by the + optional parameters devicePorts or applicationServerPorts. + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + + ApplicationProfileId: + description: Identifier for the Application Profile + type: string + format: uuid + + ApplicationServer: + type: object + minProperties: 1 + properties: + domainName: + type: string + ipv4Address: + type: string + format: ipv4 + ipv6Address: + type: string + format: ipv6 + port: + type: integer + + Protocol: + type: string + enum: + - HTTP + - MQTT3 + - MQTT5 + + EventType: + type: string + enum: + - org.camaraproject.session-insights.v0.quality-score + - org.camaraproject.session-insights.v0.network-event + - org.camaraproject.session-insights.v0.proposed-resolution + - org.camaraproject.session-insights.v0.subscription-ends + + # ---------- CloudEvents & data payloads ---------- + CloudEvent: + type: object + properties: + specversion: + type: string + enum: + - "1.0" + id: + type: string + source: + type: string + type: + $ref: "#/components/schemas/EventType" + time: + type: string + format: date-time + datacontenttype: + type: string + default: application/json + data: + type: object + required: + - specversion + - id + - source + - type + - time + - data + + SessionQualityData: + type: object + properties: + upstreamRate: + description: | + The upstream bitrate + allOf: + - $ref: "#/components/schemas/Rate" + downstreamRate: + description: | + The downstream bitrate + allOf: + - $ref: "#/components/schemas/Rate" + packetDelay: + description: | + The packet delay one-way latency between the customer's device + and the gateway from the operator's network to other networks. By limiting the delay, the network + can provide an acceptable level of performance for various services, such as voice calls, + video streaming, and data. + The end-to-end or round trip latency will be about two times this value plus the latency not controlled + by the operator + allOf: + - $ref: "#/components/schemas/Duration" + jitter: + description: | + The variation in round-trip + packet delay for the 99th percentile of traffic, following ITU Y.1540 + standards. It considers only acknowledged packets in a session, which are + packets that receive a confirmation of receipt from the recipient (e.g., + using TCP). This requirement helps maintain consistent latency, essential + for real-time applications such as VoIP, video calls, and gaming. + allOf: + - $ref: "#/components/schemas/Duration" + packetErrorLossRate: + type: integer + description: | + This field specifies the measured level of data loss during transmission. + The value is an exponent of 10, so a value of 3 means that up to 10⁻³, or 0.1%, of the + data packets may be lost. This setting is part of a broader system that categorizes + different types of network traffic (like phone calls, video streams, or data transfers) + to ensure they perform reliably on the network. + format: int32 + minimum: 1 + maximum: 10 + example: 3 + resolution: + type: string + score: + type: integer + required: + - packetDelay + - jitter + - packetErrorLossRate + - downstreamRate + - upstreamRate + - resolution + - score + + ScoreAlertData: + type: object + properties: + score: + type: integer + threshold: + type: integer + severity: + type: string + enum: + - warning + - critical + required: + - score + + ResolutionProposedData: + type: object + properties: + resolutionType: + type: string + enum: + - NETWORK_QOS + - APPLICATION_CONFIG + - OTHER + description: + type: string + required: + - resolutionType + - description + + SubscriptionEndsData: + type: object + properties: + reason: + type: string + + SessionQualityNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.quality-score + data: + $ref: "#/components/schemas/SessionQualityData" + + ScoreAlertNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.network-event + data: + $ref: "#/components/schemas/ScoreAlertData" + + ResolutionProposedNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.proposed-resolution + data: + $ref: "#/components/schemas/ResolutionProposedData" + + SubscriptionEndsNotification: + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + type: + enum: + - org.camaraproject.session-insights.v0.subscription-ends + data: + $ref: "#/components/schemas/SubscriptionEndsData" + + NotificationEvent: + oneOf: + - $ref: "#/components/schemas/SessionQualityNotification" + - $ref: "#/components/schemas/ScoreAlertNotification" + - $ref: "#/components/schemas/ResolutionProposedNotification" + - $ref: "#/components/schemas/SubscriptionEndsNotification" + discriminator: + propertyName: type + + MetricsPayload: + type: object + description: KPI message published to `metricsTopic` + properties: + latency: + type: number + format: float + jitter: + type: number + format: float + packetLoss: + type: number + bitrate: + type: number + resolution: + type: string + required: + - latency + - jitter + - packetLoss + - bitrate + - resolution + + Rate: + description: Specification of rate + type: object + properties: + value: + description: Quantity of rate + type: integer + example: 10 + format: int32 + minimum: 0 + maximum: 1024 + unit: + $ref: "#/components/schemas/RateUnitEnum" + + Duration: + description: Specification of duration + type: object + properties: + value: + description: Quantity of duration + type: integer + example: 12 + format: int32 + minimum: 1 + unit: + $ref: "#/components/schemas/TimeUnitEnum" + + TimeUnitEnum: + description: Units of time + type: string + enum: + - Days + - Hours + - Minutes + - Seconds + - Milliseconds + - Microseconds + - Nanoseconds + + RateUnitEnum: + description: Units of rate + type: string + enum: + - bps + - kbps + - Mbps + - Gbps + - Tbps + + ErrorInfo: + type: object + properties: + status: + type: integer + code: + type: string + message: + type: string + required: + - status + - code + - message + + RetrieveSessionsInput: + description: Parameters to get QoS session information by device + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + RetrieveSessionsOutput: + description: QoS session information for a given device + type: array + items: + $ref: "#/components/schemas/Session" + minItems: 0 + + + responses: + BadRequest400: + description: Bad request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + + Forbidden403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + NotFound404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Conflict409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS diff --git a/original/SessionInsights/documentation/API_documentation/SessionInsights_User_Story.md b/original/SessionInsights/documentation/API_documentation/SessionInsights_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..ff22cf999f4011f831f99154c141f8286e37b085 --- /dev/null +++ b/original/SessionInsights/documentation/API_documentation/SessionInsights_User_Story.md @@ -0,0 +1,15 @@ +# Session Insights (SI) User Story + +| **Item** | **Description** | +| ------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | +| **_Summary_** | As an application developer, I want to be able to stream my application's network KPIs to the network operator. This allows the network operator to monitor in real-time whether it is meeting these dynamic requirements, and if not, proactively suggest or implement corrective measures to maintain optimal performance. | +| **_Roles, Actor(s) and scope_** | **Roles:** API Consumer:Developer

                                                                      **Actors:** Application service providers, hyperscalers, application developers.

                                                                      **Scope:**
                                                                      • Create a Session Insights session
                                                                      • Send Network KPIs
                                                                      • Get Session Insights score
                                                                      • Get root cause and recommended corrective actions
                                                                      • End Session
                                                                      | +| **_Pre-conditions_** | The preconditions are:
                                                                      1. Customer:Developer is eligible to use the Session Insights API, i.e. the Customer has successfully subscribed to the Session Insights API on the platform of an API Provider.
                                                                      2. The customer application has requested and received an access token for the required scopes of the API.
                                                                      3. The application developer has provisioned an application profile that will be used for the Session Insights session.
                                                                      | +| **_Begins when_** | The customer application creates a Session Insights session using an application profile, device identifier or 3-legged token, and callback URI. The CSP provides a session ID in the response. | +| **_Step 1_** | The customer application periodically sends its network KPIs for its session to the CSP either via HTTP post or via MQTT. | +| **_Step 2_** | The CSP calculates a Session Insights score using a combination of the KPIs sent to it from the application along with its own network KPIs and the application profile. The CSP then sends a score back to the customer application via the callback URI provided (could be HTTP webhook, MQTT topic, or other method). | +| **_Step 3_** | The CSP can optionally include additional information along with the score to help diagnose and correct an issue when the score falls below acceptable thresholds (Root Cause). | +| **_Step 4_** | The customer application decides whether to take corrective action. | +| **_Ends when_** | The customer application ends the Session Insights session ends or times out due to inactivity. | +| **_Post-conditions_** | The customer application was able to adjust to network issues in real-time and provide consistent performance to the end user of the application. | +| **_Exceptions_** | Several exceptions might occur during the Session Insights API operations:
                                                                      • Unauthorized: Not valid credentials (i.e. use of an expired access token).
                                                                      • Conflict: Internal configuration policies didn’t allow for operations, i.e. a second Session Insights session for one device.
                                                                      • Not Found: application profile provided for session is not a defined application profile
                                                                      • Bad Request: If KPIs provided are not valid
                                                                      • Session-not-created: Due to other internal errors, Session Insights session resource could not be created. | diff --git a/original/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist.md b/original/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..3651706cefdc06e400e13ccfd956091c329fcae0 --- /dev/null +++ b/original/SessionInsights/documentation/API_documentation/session-insights-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for api-name api-version in rx.y. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                        public | stable
                                                                        public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [/code/API_definitions/session-insights.yaml](/code/API_definitions/session-insights.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | Comm. release nr | +| 3 | Guidelines from ICM applied | O | M | M | M | tbd | ICM release nr | +| 4 | API versioning convention applied | M | M | M | M | tbd | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [/documentation/API_documentation/SessionInsights_User_Story.md](/documentation/API_documentation/SessionInsights_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | N | | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | issue link | +| 10 | API release numbering convention applied | M | M | M | M | tbd | | +| 11 | Change log updated | M | M | M | M | tbd | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | comment | +| 13 | API description (for marketing) | O | O | M | M | Y | [https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/94011619/SessionInsights](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/94011619/SessionInsights) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/ShortMessageService/README.md b/original/ShortMessageService/README.md new file mode 100644 index 0000000000000000000000000000000000000000..a569130fcf20abc7ffc8547758d6f71837d48209 --- /dev/null +++ b/original/ShortMessageService/README.md @@ -0,0 +1,42 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#285](https://github.com/camaraproject/APIBacklog/issues/285) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase C – Repository With Partial Progress](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# ShortMessageService + +Sandbox API Repository to describe, develop, document, and test the ShortMessageService Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/wSne) + +## Scope +* Service APIs for “Short Message Service” (see APIBacklog.md) +* It provides the customer with the ability to: + * to send SMS to the destination address(es). There are 3 different categories of SMS i.e. Service, Promotional & Transactional. This API is used to send all categories of messages. Pre-requisite for using this API is that SMS Sender application / enterprise (or customer) needs to onboard itself with the access provider before using this API. This API has only single operation i.e. Send SMS - Provides the capability to deliver SMS to the recepient. In order to the receive delivery receipt separate API to be defined which is to be implemented by the API consumer for sending back the delivery receipt to the 'Send SMS' API consumer in a standardized callback API. + * NOTE: The scope of these APIs should be limited (at least at a first stage) to 4G and 5G. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Location: virtually + +## Meetings +* Meetings are held virtually +* Schedule: tbd +* Meeting link: tbd + +## Contributorship and mailing list +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/original/ShortMessageService/code/API_definitions/README.MD b/original/ShortMessageService/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/ShortMessageService/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/ShortMessageService/code/API_definitions/SMS.yaml b/original/ShortMessageService/code/API_definitions/SMS.yaml new file mode 100644 index 0000000000000000000000000000000000000000..e6f15327818fc197c244615f023b940fa32434eb --- /dev/null +++ b/original/ShortMessageService/code/API_definitions/SMS.yaml @@ -0,0 +1,268 @@ +openapi: 3.0.3 +info: + title: SMS API + description: | + The API provides the customer with the ability to send SMS to the recepient address(es). + Customer can use this API to send SMS in following scenarios: + 1. Application server needs to send text message to a recepient number which is being used on a mobile phone device. There are 3 different categories of text SMS i.e. Service, Promotion & Transaction. + 2. Application server needs to send binary message to a recepient number which is being used on (IoT) device. + + Pre-requisite for using this API is that SMS Sender application / enterprise (or customer) needs to onboard themselves with the access provider before using this API. + This API has single operation to send SMS. + + In order to the receive delivery receipt, separate API to be subscribed by the API consumer for receiving the delivery receipt in a standardized callback API. + + # Authorization and authentication + CAMARA guidelines defines a set of authorization flows which can grant API clients access to the API functionality, as outlined in the document [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md). Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + version: 0.1.0-alpha.1 + termsOfService: http://example.com/terms/ + contact: + name: API Support + url: http://www.example.com/support + email: support@example.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/ShortMessageService +servers: + - url: '{apiRoot}/{basePath}' + variables: + apiRoot: + default: http://localhost:9091 + description: API root + basePath: + default: sms/v0alpha1 + description: Base path for the Short Message Service +tags: + - name: Short Message Service + description: API operation to send SMS +paths: + /short-message: + post: + security: + - openId: + - send-sms:short-message + tags: + - Send SMS + summary: Send SMS + description: | + The customer application server makes a request to the SMS API to send SMS message to the destination address. + operationId: send-sms + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Submit a request for sending SMS to the destination address + content: + application/json: + schema: + $ref: '#/components/schemas/MessageRequest' + examples: + MessageRequest: + value: + to: ['+910123456789'] + from: '+919876543210' + category: PROMOTION + message: xxxxxxxxxx + required: true + responses: + '200': + $ref: '#/components/responses/Generic200' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + schemas: + MessageRequest: + type: object + required: + - to + - from + - message + properties: + to: + type: array + description: "The recipients MSISDN" + items: + type: string + from: + type: string + description: "The senders MSISDN" + category: + type: string + enum: ["PROMOTION","SERVICE","TRANSACTION"] + message: + type: string + description: "SMS message" + MessageResponse: + type: object + required: + - msgId + - timestamp + properties: + msgId: + type: string + description: "The SMS messages sent to the recipients are identified by smsnumber are identified." + timestamp: + type: string + format: date-time + description: Timestamp when SMS was delivered. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + ErrorInfo: + type: object + required: + - status + - code + - detail + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + detail: + type: string + description: Detailed error description + responses: + Generic200: + description: OK + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/MessageResponse' + example: + msgId: 56647d96-b3e6-48d2-b93f-ab0d56bdd965 + timestamp: "2024-03-19T12:33:27.070Z" + + Generic400: + description: Problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + detail: Client specified an invalid argument, request body or query param + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + detail: Request not authenticated due to missing, invalid, or expired credentials + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + detail: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + detail: Phone number cannot be deducted from access token context + Generic404: + description: Resource Not Found + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + detail: A specified resource is not found + Generic500: + description: Server error + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + detail: Server error + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + detail: Service unavailable diff --git a/original/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription.yaml b/original/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription.yaml new file mode 100644 index 0000000000000000000000000000000000000000..2fd15c0d08afcd0e87f13302801831efaffe1ff9 --- /dev/null +++ b/original/ShortMessageService/code/API_definitions/sms-delivery-notification-subscription.yaml @@ -0,0 +1,735 @@ +openapi: 3.0.3 +info: + title: SMS Delivery Notification Subscription + description: | + API to create, retrieve and delete event subscriptions related to a sms delivery operation performed on an associated phone number. + + # Introduction + + With this API, customers can create subscriptions for receiving delivery notification on the requests sent. + + The consumer id in the request gives the identity of the consumer for which call back notification subscription to be enabled. + + Upon successfully creating a subscription, the API will provide an Event Subscription ID, and it will indicate the subscription's expiration date. + + After delivering the SMS, the event subscriber will be notified back to the provided Notification-Url given by the subscription-request. + + SMS delivery notification API could be useful in scenarios such as: + + - Reconciliation (by the API consumer) on the number of messages sent vs delivered. + + # Relevant terms and definitions + + # API Functionality + + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows CloudEvents specification. + + It is mandatory in the subscription to provide the event `type` for which the client would like to subscribe. + + Following event ``type`` are managed for this API: + - ``org.camaraproject.sms.v0.-status`` - Event triggered when the sms delivery task is completed by the server + + Note: Additionally to these list, ``org.camaraproject.sms.v0.subscription-ends`` notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used when: + - the subscription expire time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the API server has to stop sending notification prematurely + + + + The API exposes following capabilities: + * **/subscriptions**: This endpoint has two operations, one that allows to retrieve the list of SMS delivery event subscriptions and another one to create new event subscriptions. + * **/subscriptions/{subscriptionId}**: This endpoint also has two operations, one that allows to retrieve a particular event subscription by id and another one to delete an event subscription also using the id. + + ## SMS delivery notification subscription + + Theses endpoints allow to manage notification subscription on Send SMS delivery event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows Cloudevents specification. + + It is mandatory in the subscription to provide the event `type` subscribed are several are managed in this API. + + Only one event ``type`` is managed for this API: + - ``org.camaraproject.sms.v0.sms-delivery-status`` - Event triggered when a sms delivery event occurs on the any request given by the consumer + + + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as `POST /{$request.body#/webhook/notificationUrl}` + will be posted by the sim swap resource server to the webhook url provided by notification + listener. + + # Authorization and authentication + + CAMARA guidelines defines a set of authorization flows which can grant API clients access to the API functionality, as outlined in the document [CAMARA-API-access-and-user-consent.md](https://github.com/camaraproject/IdentityAndConsentManagement/blob/main/documentation/CAMARA-API-access-and-user-consent.md). Which specific authorization flows are to be used will be determined during onboarding process, happening between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, while also being subject to the prevailing legal framework dictated by local legislation. + + It is important to remark that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + termsOfService: http://swagger.io/terms/ + contact: + email: project-email@sample.com + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.1.0-alpha.1 +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/sendsms +servers: + - url: '{apiRoot}/sms-delivery-notification-subscriptions/v0alpha1' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: SMS delivery notification subscription + description: Operation to manage event subscription on sms delivery event (swapped) + +paths: + /subscriptions: + post: + tags: + - SMS delivery notification subscription + summary: 'Create a sms delivery event subscription for a given consumer' + description: Create a sms delivery event subscription for a given consumer + operationId: createSMSDeliverySubscription + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - sms-delivery:subscriptions:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/CreateSubscription' + required: true + callbacks: + notifications: + "{$request.body#/webhook/notificationUrl}": + post: + tags: + - Session notifications callback + summary: "Session notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The sim swap server will call this endpoint whenever a swapped event occurs. + operationId: postNotification + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + STATUS: + $ref: '#/components/examples/STATUS' + SUBSCRIPTION_ENDS: + $ref: '#/components/examples/SUBSCRIPTION_ENDS' + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + security: + - { } + - notificationsBearerAuth: [ ] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionInfo' + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionAsync' + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "409": + $ref: '#/components/responses/Generic409' + "500": + $ref: '#/components/responses/Generic500' + "503": + $ref: '#/components/responses/Generic503' + get: + tags: + - SMS Delivery notification subscription + summary: 'Retrieve a list of SMS Delivery event subscription' + description: Retrieve a list of SMS Delivery event subscription(s) + operationId: retrieveSubscriptionList + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - sim-swap:subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: '#/components/schemas/SubscriptionInfo' + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "500": + $ref: '#/components/responses/Generic500' + "503": + $ref: '#/components/responses/Generic503' + /subscriptions/{subscriptionId}: + get: + tags: + - SMS Delivery notification subscription + summary: 'Retrieve a sms delivery event subscription for a phone number' + description: retrieve event subscription information for a given subscription. + operationId: retrieveSubscription + security: + - openId: + - sim-swap:subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "200": + description: OK + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionInfo' + "400": + $ref: '#/components/responses/SubscriptionIdRequired' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + delete: + tags: + - SMS Delivery notification subscription + summary: 'Delete a sms delivery event subscription' + operationId: deleteSubscription + description: delete a given event subscription. + security: + - openId: + - sim-swap:subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: '#/components/parameters/x-correlator' + responses: + "204": + description: event subscription deleted + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/SubscriptionAsync' + "400": + $ref: '#/components/responses/SubscriptionIdRequired' + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: '#/components/schemas/SubscriptionId' + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + schemas: + SenderId: + type: string + description: "Identifer for the matching criteria basis which call back would be triggered by the server. In this case it would be the message sender id." + example: 'AD-HDFCBK' + + MsgId: + type: string +# pattern: '^\+[1-9][0-9]{4,14}$' + example: '56647d96-b3e6-48d2-b93f-ab0d56bdd965' + description: "Every request from sender application to send SMS to recepient is acknowledged with a MsgId. This MsgId is sent in the call back." + + Status: + type: string + example: 'SUCCESS' + description: "Every request from sender application to send SMS to recepient is acknowledged with a MsgId. This MsgId is sent in the call back." + enum: + - SUCCESS + - FAIL + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + CreateSubscription: + description: The request for creating a sim swap event subscription + type: object + required: + - webhook + - subscriptionDetail + properties: + subscriptionDetail: + $ref: '#/components/schemas/SubscriptionDetail' + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time in date-time format. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) - Once this number is reached, the subscription ends. -1 means there is no limit. + example: -1 + webhook: + $ref: '#/components/schemas/Webhook' + + Webhook: + description: Webhook information for event channel + type: object + required: + - notificationUrl + properties: + notificationUrl: + type: string + example: "https://application-server.com" + description: https callback address where the event notification must be POST-ed + notificationAuthToken: + type: string + example: "c8974e592c2fa383d4a3960714" + description: | + OAuth2 token to be used by the callback API endpoint. It MUST be indicated within HTTP Authorization header e.g. Authorization: Bearer $notificationAuthToken + + SubscriptionDetail: + type: object + description: The detail of the requested event subscription + required: + - senderId + - type + properties: + senderId: + $ref: '#/components/schemas/SenderId' + type: + $ref: '#/components/schemas/SmsDeliveryNotificationEventType' + +# CreateSubscriptionDetail: +# description: The detail of the requested event subscription +# type: object +# required: +# - type +# properties: +# msgId: +# $ref: '#/components/schemas/MsgId' +# type: +# $ref: '#/components/schemas/SendSMSEventType' + +# SendSMSEventType: +# type: string +# description: | +# sms-delivery-status - Event triggered when a sms-delivery action is complete and delivery status is to be returned back. + +# enum: +# - org.camaraproject.sms.v0.sms-delivery-status + + SmsDeliveryNotificationEventType: + type: string + description: | + sms-delivery - Event triggered after sms-delivery task is complete. This sms-delivery tasks completion may have status/outcome as success or failure which is returned back in callback to the requestor. + + enum: + - org.camaraproject.sms.v0.sms-delivery-status + + SubscriptionInfo: + description: Represents a sim swaps subscription. + required: + - startsAt + - subscriptionId + allOf: + - $ref: '#/components/schemas/CreateSubscription' + - type: object + properties: + subscriptionId: + $ref: '#/components/schemas/SubscriptionId' + subscriptionDetail: + $ref: '#/components/schemas/SubscriptionDetail' + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time in date-time format. + webhook: + $ref: '#/components/schemas/Webhook' + startsAt: + type: string + format: date-time + description: date time when subscription started + expiresAt: + type: string + format: date-time + description: date time when subscription will expire or expired + required: + - eventSubscriptionId + - type + + SubscriptionAsync: + description: Response for a sim swap operation managed asynchronously (Creation or Deletion) + type: object + properties: + subscriptionId: + $ref: '#/components/schemas/SubscriptionId' + + SubscriptionId: + type: string + description: The event subscription identifier. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - data + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: '#/components/schemas/Source' + type: + $ref: '#/components/schemas/SmsDeliveryNotificationEventType' + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + example: 1.0 + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + example: application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: 'type' + mapping: + org.camaraproject.sms.v0.sms-delivery-status: '#/components/schemas/EventSimSwap' + org.camaraproject.sms.v0.subscription-ends: '#/components/schemas/EventSimSwapSubscriptionEnds' + + Source: + type: string + format: uri-reference + minLength: 1 + description: "Identifies the context in which an event happened in the specific Provider Implementation." + example: + - https://github.com/cloudevents + - mailto:cncf-wg-serverless@lists.cncf.io + - urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - cloudevents/spec/pull/123 + - /sensors/tn-1234567/alerts + - 1-555-123-4567 + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. Must adhere to RFC 3339. + example: '2018-04-05T17:31:00Z' + + EventSimSwap: + description: event structure for swapped event + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + properties: + data: + $ref: '#/components/schemas/DeliveryStatus' + + EventSimSwapSubscriptionEnds: + description: event structure for event subscription ends + allOf: + - $ref: '#/components/schemas/CloudEvent' + - type: object + required: + - data + properties: + data: + $ref: '#/components/schemas/SubscriptionEnds' + + DeliveryStatus: + description: Event detail structure for SMS Delivery event. + type : object + required: + - msgId + - subscriptionId + properties: + msgId: + $ref: '#/components/schemas/MsgId' + status: + $ref: '#/components/schemas/Status' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnds: + description: Event detail structure for SUBSCRIPTION_ENDS event + type : object + required: + - msgId + - terminationReason + - subscriptionId + properties: + msgId: + $ref: '#/components/schemas/MsgId' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + + + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: "INVALID_ARGUMENT" + message: "Client specified an invalid argument, request body or query param" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: "UNAUTHENTICATED" + message: "Request not authenticated due to missing, invalid, or expired credentials" + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: "PERMISSION_DENIED" + message: "Client does not have sufficient permissions to perform this action" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: "The specified resource is not found" + Generic409: + description: Conflict + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: CONFLICT + message: "The specified resource is in a conflict" + Generic500: + description: Server error + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: "INTERNAL" + message: "Server error" + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: "UNAVAILABLE" + message: "Service unavailable" + SubscriptionIdRequired: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + Generic400: + summary: Schema validation failed + value: + status: 400 + code: INVALID_ARGUMENT + message: "Client specified an invalid argument, request body or query param" + subscriptionIdRequired: + summary: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + examples: + STATUS: + value: + id: 123655 + source: supertelco.notificationSendServer12 + type: org.camaraproject.sms.v0.sms-delivery-status + specversion: "1.0" + datacontenttype: application/json + data: + msgId: 56647d96-b3e6-48d2-b93f-ab0d56bdd965 + subscriptionId: 2ghy-55gg-7iup-yuo9 + time: 2023-01-18T13:18:23.682Z + + SUBSCRIPTION_ENDS: + value: + id: 123658 + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap.v0.subscription-ends + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: +123456789 + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: 2ghy-55gg-7iup-yuo9 + terminationDescription: subscription expire time reached + time: 2023-01-19T13:18:23.682Z diff --git a/original/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story.md b/original/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..a8c0183b2874058c19b447e253547dfcf58d2fe8 --- /dev/null +++ b/original/ShortMessageService/documentation/API_documentation/Text_SMS_User_Story.md @@ -0,0 +1,13 @@ +**User Story: Send Text SMS from channels/applications to the destination address(es) via network operator. ** +
                                                                        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to send SMS from channels/applications to the destination address(es) via network operator. There are 3 different categories of SMS i.e. Service, Promotional & Transactional. This API is used to send all categories of messages. | +| ***Roles, Actors and Scope*** | **Roles:** Application Server (of developer)
                                                                        **Actors:** SMS API Consumer (Application Server, Mobile App, Machine), SMS API Provider (Mobile Network Operator or MNO, Hyperscalers), SMS Destination (Machine, Mobile Device)
                                                                        **Scope:** To send text SMS to the destination address(s) | +| ***Pre-conditions*** |Pre-requisite for using this API are:
                                                                        1. SMS Sender application / enterprise (or customer) is onboarded itself with the access provider before using this API
                                                                        2. SMS Sender application / enterprise (or customer) has the API credentials.
                                                                        | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the SMS API to send text SMS to the destination address.
                                                                        **Ends when:** The destination receives the text SMS.
                                                                        | +| ***Post-conditions*** | The SMS is successfully delivered to the destination address.| +| ***Exceptions*** | Several exceptions might occur during the SMS API operations:
                                                                        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                        • Not Found: The number provided is not managed by the MNO
                                                                        • Invalid input: Not all mandatory input data to invoke operation (e.g. format not as expected).
                                                                        • Conflict: Internal configuration policies didn’t allow for operations.
                                                                        • Not Allowed: Message sending restricted (DND).
                                                                        | + +

                                                                        \ No newline at end of file diff --git a/original/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story.MD b/original/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story.MD new file mode 100644 index 0000000000000000000000000000000000000000..6453817059213be2fd6f81e10478752e739fa2d5 --- /dev/null +++ b/original/ShortMessageService/documentation/API_documentation/binary_SMS_User_Story.MD @@ -0,0 +1,13 @@ +**User Story: Send binary SMS message to communication module** +
                                                                        + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to remotely control a product equipped with a communication module, so I want to send a binary SMS message of control commands to it. | +| ***Roles, Actors and Scope*** | **Roles:** Application Developer
                                                                        **Actors:** Mobile Network Operators (MNO), hyperscalers, application developers, enterprise.
                                                                        **Scope:** To send binary SMS message to the destination address of the communication module | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                        1. Application developer has onboarded to MNO API
                                                                        2. Application developer has API credentials
                                                                        | +| ***Activities/Steps*** | **Starts when:** The customer application server makes a request to the SMS API to send binary SMS message to the destination address of the communication module.
                                                                        **Ends when:** The communication module receives the binary SMS message.
                                                                        | +| ***Post-conditions*** | The comand in the binay SMS message works on the application of the product equipped with the communication module.| +| ***Exceptions*** | Several exceptions might occur during the SMS API operations:
                                                                        • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                        • Not Found: The number provided is not managed by the MNO
                                                                        • Invalid input: Not all mandatory input data to invoke operation (e.g. format not as expected).
                                                                        • Conflict: Internal configuration policies didn’t allow for operations.
                                                                        | + +

                                                                        diff --git a/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18.md b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18.md new file mode 100644 index 0000000000000000000000000000000000000000..518a3605562a47862002f1af69f0b126fa5ccaed --- /dev/null +++ b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-18.md @@ -0,0 +1,30 @@ +# Short Messaging Service meeting + +#### *January 24, 2024* + +
                                                                        + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla, Gaurav Pandey, Rahul Mehta, Hitesh Dalal | +| KDDI | Tetsuya Chiba | +---- + +
                                                                        + +## Agenda + +1. Introductions +2. Defining Ways Of Working + +
                                                                        + +## Points of Discussion +- Define the User Stories for SMS and then move to defining the API specification + +## AoB + +- Next call schedule: January 24, 2024. diff --git a/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24.md b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24.md new file mode 100644 index 0000000000000000000000000000000000000000..6dfb7e0430af9b50af07a38e07e67a8e0a20dee9 --- /dev/null +++ b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-24.md @@ -0,0 +1,32 @@ +# Short Messaging Service meeting + +#### *January 24, 2024* + +
                                                                        + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla, Rahul Mehta, Hitesh Dalal | +| KDDI | Tetsuya Chiba | +---- + +
                                                                        + +## Agenda + +1. Introductions +2. Discussion on the API scope + +
                                                                        + +## Points of Discussion +- Discussion on how this API is different from OTP validation API. +- Agreement on using this API for Binary Message +- Defining 2 User Stories for SMS API (Text & Binary SMS) + +## AoB + +- Next call schedule: January 31, 2024. diff --git a/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31.md b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31.md new file mode 100644 index 0000000000000000000000000000000000000000..860f48e8577b62ae19288e9825cf5c221cd99bbd --- /dev/null +++ b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-01-31.md @@ -0,0 +1,30 @@ +# Short Messaging Service meeting + +#### *January 31, 2024* + +
                                                                        + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla | +| KDDI | Tetsuya Chiba | +---- + +
                                                                        + +## Agenda + +1. Introductions +2. User Story Discussion + +
                                                                        + +## Points of Discussion +- Alignment on the template for documenting User Stories + +## AoB + +- Next call schedule: February 7, 2024. diff --git a/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07.md b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07.md new file mode 100644 index 0000000000000000000000000000000000000000..05375749c084dc5d9688217fd7a8a10a3227b0b4 --- /dev/null +++ b/original/ShortMessageService/documentation/MeetingMinutes/2024/MOM-2024-02-07.md @@ -0,0 +1,29 @@ +# Short Messaging Service meeting + +#### *January 31, 2024* + +
                                                                        + +## Attendees + + +| Companies | Attendees | +| --------- | --------- | +| Airtel | Ramit Chawla | +| KDDI | Tetsuya Chiba | +---- + +
                                                                        + +## Agenda + +- User Story Discussion + +
                                                                        + +## Points of Discussion +- Walkthrough of the Text Message user story + +## AoB + +- Next call schedule: February 7, 2024. diff --git a/original/ShortMessageService/documentation/MeetingMinutes/README.MD b/original/ShortMessageService/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..ef8599de6faab6222614dfcd2dc5d8e09248c6f3 --- /dev/null +++ b/original/ShortMessageService/documentation/MeetingMinutes/README.MD @@ -0,0 +1,7 @@ +This README.MD can be deleted when the first file is added to this directory. +24-Jan-2024 + +31-Jan-2024 + +7-Feb-2024 + diff --git a/original/ShortMessageService/documentation/SupportingDocuments/README.MD b/original/ShortMessageService/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/ShortMessageService/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SimSwap/README.md b/original/SimSwap/README.md new file mode 100644 index 0000000000000000000000000000000000000000..142835493d61ea4ebbd193856b60d93a7da6e5fd --- /dev/null +++ b/original/SimSwap/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# SimSwap + +Incubating API Repository to evolve and maintain the definitions and documentation of SimSwap Service APIs within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/0jXe) + +## Scope + +* Service APIs for “SimSwap” (see APIBacklog.md) +* The APIs provide the API consumer with the ability to: + * obtain information on any recent SIM pairing change related to the User’s mobile account. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: October 2022 +* Incubating stage since: February 2025 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r3.3](https://github.com/camaraproject/SimSwap/releases/tag/r3.3) (Fall25), with the following API versions: + * **sim-swap-subscriptions v0.3.0** + [[YAML]](https://github.com/camaraproject/SimSwap/blob/r3.3/code/API_definitions/sim-swap-subscriptions.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap-subscriptions.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap-subscriptions.yaml) + * **sim-swap v2.1.0** + [[YAML]](https://github.com/camaraproject/SimSwap/blob/r3.3/code/API_definitions/sim-swap.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimSwap/r3.3/code/API_definitions/sim-swap.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SimSwap/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SimSwap/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SimSwap/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing + +* Meetings are held virtually + * Schedule: Every 4 weeks, Thursday, 7:30 AM UTC (8:30 CET/9:30 CEST) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94893248838?password=05b2197d-309e-41ef-aadf-639f71ef7f38) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/hDze) +* Mailing List: + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/SimSwap/code/API_definitions/sim-swap-subscriptions.yaml b/original/SimSwap/code/API_definitions/sim-swap-subscriptions.yaml new file mode 100644 index 0000000000000000000000000000000000000000..20b0c3808f7c1fc8e33bb11ee68e66114a406ce0 --- /dev/null +++ b/original/SimSwap/code/API_definitions/sim-swap-subscriptions.yaml @@ -0,0 +1,1456 @@ +openapi: 3.0.3 +info: + title: Sim Swap Subscriptions + description: | + This API provides the customer with the ability to subscribe to event related to a sim swap operation performed on an associated phone number. + + # Introduction + + This API empowers service providers and network operators with a seamless mechanism for managing and monitoring SIM card swaps, a process often used in legitimate device upgrades or replacements but also susceptible to abuse in fraudulent activities. + + # Relevant terms and definitions + + * **SIM swap**: + A SIM swap is a process in which a mobile phone user's current SIM card is deactivated or replaced with a new one. This is typically done by contacting the user's mobile service provider and requesting a new SIM card for various reasons, such as a lost or damaged SIM card, upgrading to a new phone, or changing phone numbers while keeping the same device. + + # API Functionality + + The API exposes following capabilities: + * **/subscriptions**: This endpoint has two operations, one that allows to retrieve the list of Sim Swap event subscriptions and another one to create new event subscriptions. + * **/subscriptions/{subscriptionId}**: This endpoint also has two operations, one that allows to retrieve a particular event subscription by id and another one to delete an event subscription also using the id. + + ## Sim Swap notification subscription + + Theses endpoints allow to manage notification subscription on Sim Swap event. + The CAMARA subscription model is detailed in the CAMARA API design guideline document and follows Cloudevents specification. + + It is mandatory in the subscription to provide the event `types` subscribed are several are managed in this API. + + Only one event ``types`` is managed for this API: + - ``org.camaraproject.sim-swap-subscriptions.v0.swapped`` - Event triggered when a sim swap occurs on the associated phoneNumber + + + Note: Additionally to these list, ``org.camaraproject.sim-swap-subscriptions.v0.subscription-ended`` notification `types` is sent when the subscription ends. + This notification does not require dedicated subscription. + It is used when: + - the subscription expiration time (optionally set by the requester) has been reached + - the maximum number of subscription events (optionally set by the requester) has been reached + - the subscription was deleted by the requester + - the API server has to stop sending notification prematurely + - the Access Token sinkCredential expiration time (set by the requester) has been reached + + ### Notification callback + + This endpoint describes the event notification received on subscription listener side when the event occurred. As for subscription, detailed description of the event notification is provided in the CAMARA API design guideline document. + + **WARNING**: This callback endpoint must be exposed on the listener side as `POST /{$request.body#/sink}` + will be posted by the sim swap resource server to the webhook url provided by notification + listener. + + ### Data Minimization + + #### phoneNumber presence: + These rules apply for subscription: + + - If 3-legged access token is used, the POST and GET{id} requests & responses must NOT provide the ``phoneNumber``. For GET (list) only subscription(s) for this exactly phone number is/are retrieved (implicit filtering). + - If 2-legged access token is used, for POST and GET{id}, the presence of ``phoneNumber`` in the request & response is mandatory. For GET (list) the device identifier (``phoneNumber``) could be used as filtering criteria. + + #### sinkCredential presence: + + ``sinkCredential`` is only present in POST request and not provided in POST or GET response. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the provider of the application consuming the API and the operator's API exposure platform, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/ +servers: + - url: '{apiRoot}/sim-swap-subscriptions/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Sim Swap Subscription + description: Operation to manage event subscription on sim swap event (swapped) + +paths: + /subscriptions: + post: + tags: + - Sim Swap Subscription + summary: 'Create a sim swap event subscription for a phone number' + description: Create a sim swap event subscription for a phone number + operationId: createSimSwapSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - sim-swap-subscriptions:org.camaraproject.sim-swap-subscriptions.v0.swapped:create + + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + SUBSCRIPTION_REQUEST: + $ref: '#/components/examples/SUBSCRIPTION_REQUEST' + SUBSCRIPTION_REQUEST_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_REQUEST_3LEGS' + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: | + Important: this endpoint is to be implemented by the API consumer. + The sim swap server will call this endpoint whenever a swapped event occurs. + operationId: postNotification + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + SWAPPED: + $ref: '#/components/examples/SWAPPED' + SUBSCRIPTION_ENDS: + $ref: '#/components/examples/SUBSCRIPTION_ENDS' + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + SUBSCRIPTION_RESPONSE: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE' + SUBSCRIPTION_RESPONSE_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE_3LEGS' + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Sim Swap Subscription + summary: 'Retrieve a list of sim swap event subscription' + description: Retrieve a list of sim swap event subscription(s) + operationId: retrieveSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - sim-swap-subscriptions:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + examples: + SUBSCRIPTIONS: + $ref: '#/components/examples/SUBSCRIPTIONS' + SUBSCRIPTIONS_3LEGS: + $ref: '#/components/examples/SUBSCRIPTIONS_3LEGS' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Sim Swap Subscription + summary: 'Retrieve a sim swap event subscription for a phone number' + description: retrieve event subscription information for a given subscription. + operationId: retrieveSubscription + security: + - openId: + - sim-swap-subscriptions:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + examples: + SUBSCRIPTION: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE' + SUBSCRIPTION_3LEGS: + $ref: '#/components/examples/SUBSCRIPTION_RESPONSE_3LEGS' + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Sim Swap Subscription + summary: 'Delete a sim swap event subscription' + operationId: deleteSubscription + description: delete a given event subscription. + security: + - openId: + - sim-swap-subscriptions:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: Sim swap notification subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+123456789' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + SubscriptionRequest: + description: The request for creating a sim swap event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible for subscription: + - org.camaraproject.sim-swap-subscriptions.v0.swapped: receive a notification when a sim swap is performed on the line. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + + SubscriptionEventType: + type: string + description: | + swapped - Event triggered when a sim swap occurs on the line + enum: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + + Protocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime` or `subscriptionMaxEvents` to limit subscription lifetime. + Event type attributes must be defined in `subscriptionDetail` + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2025-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: | + Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. + minimum: 1 + example: 5 + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: "The type of the credential. With the current API version the type MUST be set to ACCESSTOKEN." + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + + SubscriptionDetail: + description: The detail of the requested event subscription + type: object + required: + - phoneNumber + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + + CreateSubscriptionDetail: + description: The detail of the requested event subscription + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + + SimSwapNotificationEventType: + type: string + description: | + swapped - Event triggered when a sim swap was performed for this phone number + + - subscription-started: Event triggered when the subscription starts + - subscription-updated: Event triggered when the subscription is updated + - subscription-ended: Event triggered when the subscription ends + enum: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + - org.camaraproject.api-name.v0.subscription-started + - org.camaraproject.api-name.v0.subscription-updated + - org.camaraproject.sim-swap-subscriptions.v0.subscription-ended + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: | + Camara Event types eligible for subscription: + - org.camaraproject.sim-swap-subscriptions.v0.swapped: receive a notification when a sim swap is performed on the line. + Note: for the Commonalities meta-release v0.4 we enforce to have only event type per subscription then for following meta-release use of array MUST be decided + at API project level. + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: "#/components/schemas/SubscriptionId" + startsAt: + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + type: string + format: date-time + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its metainformation is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + MQTT3: '#/components/schemas/MQTTSubscriptionResponse' + MQTT5: '#/components/schemas/MQTTSubscriptionResponse' + AMQP: '#/components/schemas/AMQPSubscriptionResponse' + NATS: '#/components/schemas/NATSSubscriptionResponse' + KAFKA: '#/components/schemas/ApacheKafkaSubscriptionResponse' + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as subscriptionId as per Commonalities Event Notification Model. + example: qs15-h556-rt89-1298 + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + $ref: "#/components/schemas/SimSwapNotificationEventType" + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.sim-swap-subscriptions.v0.swapped: '#/components/schemas/EventSimSwap' + org.camaraproject.sim-swap-subscriptions.v0.subscription-started: "#/components/schemas/EventSubscriptionStarted" + org.camaraproject.sim-swap-subscriptions.v0.subscription-updated: "#/components/schemas/EventSubscriptionUpdated" + org.camaraproject.sim-swap-subscriptions.v0.subscription-ended: '#/components/schemas/EventSubscriptionEnded' + + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened, as a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: Timestamp of when the occurrence happened. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + EventSimSwap: + description: event structure for event sim swapped + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/Swapped" + + EventSubscriptionStarted: + description: event structure for event subscription started + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionStarted" + + SubscriptionStarted: + description: Event detail structure for subscription started event + type: object + required: + - initiationReason + - subscriptionId + properties: + initiationReason: + $ref: "#/components/schemas/InitiationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + initiationDescription: + type: string + + InitiationReason: + type: string + description: | + - SUBSCRIPTION_CREATED - Subscription created by API Server + enum: + - SUBSCRIPTION_CREATED + + EventSubscriptionUpdated: + description: event structure for event subscription updated + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionUpdated" + + SubscriptionUpdated: + description: Event detail structure for subscription updated event + type: object + required: + - updateReason + - subscriptionId + properties: + updateReason: + $ref: "#/components/schemas/UpdateReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + updateDescription: + type: string + + UpdateReason: + type: string + description: | + - SUBSCRIPTION_ACTIVE - API server transitioned susbcription status to `ACTIVE` + - SUBSCRIPTION_INACTIVE - API server transitioned susbcription status to `INACTIVE` + enum: + - SUBSCRIPTION_ACTIVE + - SUBSCRIPTION_INACTIVE + + EventSubscriptionEnded: + description: event structure for event subscription ended + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + + Swapped: + description: Event detail structure for ROAMING_ON & ROAMING_OFF event + type: object + required: + - subscriptionId + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionEnded: + description: Event detail structure for subscription ended event + type: object + required: + - terminationReason + - subscriptionId + properties: + terminationReason: + $ref: "#/components/schemas/TerminationReason" + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationDescription: + description: Explanation why a subscription ended or had to end. + type: string + + TerminationReason: + type: string + description: | + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + MQTTSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/MQTTSettings" + + MQTTSettings: + type: object + properties: + topicName: + type: string + qos: + type: integer + format: int32 + retain: + type: boolean + expiry: + type: integer + format: int32 + userProperties: + type: object + required: + - topicName + + AMQPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/AMQPSettings" + + AMQPSettings: + type: object + properties: + address: + type: string + linkName: + type: string + senderSettlementMode: + type: string + enum: ["settled", "unsettled"] + linkProperties: + type: object + additionalProperties: + type: string + + ApacheKafkaSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/ApacheKafkaSettings" + + ApacheKafkaSettings: + type: object + properties: + topicName: + type: string + partitionKeyExtractor: + type: string + clientId: + type: string + ackMode: + type: integer + required: + - topicName + + NATSSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/NATSSettings" + + NATSSettings: + type: object + properties: + subject: + type: string + required: + - subject + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + X-Correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + SWAPPED: + value: + id: "123655" + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap-subscriptions.v0.swapped + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: "+123456788" + subscriptionId: 2ghy-55gg-7iup-yuo9 + time: 2023-01-18T13:18:23.682Z + + SUBSCRIPTION_ENDS: + value: + id: "123658" + source: supertelco.notificationSendServer12 + type: org.camaraproject.sim-swap-subscriptions.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + data: + phoneNumber: "+123456789" + terminationReason: SUBSCRIPTION_EXPIRED + subscriptionId: 2ghy-55gg-7iup-yuo9 + terminationDescription: subscription expire time reached + time: 2023-01-19T13:18:23.682Z + + SUBSCRIPTION_REQUEST: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionMaxEvents: 10 + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + SUBSCRIPTION_REQUEST_3LEGS: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + sinkCredential: + credentialType: ACCESSTOKEN + accessToken: "yJ2ZXIiOiIxLjAiLCJ0eXAiO..." + accessTokenExpiresUtc: "1717753038" + accessTokenType: "bearer" + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + SUBSCRIPTION_RESPONSE: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTION_RESPONSE_3LEGS: + value: + protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTIONS: + value: + - protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: + phoneNumber: "+123456789" + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED + SUBSCRIPTIONS_3LEGS: + value: + - protocol: HTTP + sink: https://endpoint.example.com/sink + types: + - org.camaraproject.sim-swap-subscriptions.v0.swapped + config: + subscriptionDetail: {} + + subscriptionExpireTime: '2025-01-17T13:18:23.682Z' + id: '1119920371' + startsAt: '2024-06-07T16:10:15.302Z' + expiresAt: '2024-06-07T16:10:15.302Z' + status: ACTIVATION_REQUESTED diff --git a/original/SimSwap/code/API_definitions/sim-swap.yaml b/original/SimSwap/code/API_definitions/sim-swap.yaml new file mode 100644 index 0000000000000000000000000000000000000000..8de8caa68ca755e76c79e859c6a51726b04e6179 --- /dev/null +++ b/original/SimSwap/code/API_definitions/sim-swap.yaml @@ -0,0 +1,494 @@ +openapi: 3.0.3 +info: + title: SIM Swap + description: | + The SIM swap API provides a programmable interface for developers and other users (capabilities consumers) to request the last date of a SIM swap performed on the mobile line, or, to check whether a SIM swap has been performed during a past period. + + # Introduction + + The SIM Swap API performs real-time checks on the last SIM Swap event. + + The SIM Swap API is useful to prevent fraud by reducing the risk of account takeover fraud by strengthening SIM based authentication processes such as SMS One-time passwords. Fraudsters are using SIM swap techniques to intercept SMS messages and reset passwords or receive verification codes that allow them to access protected accounts. + + The SIM Swap API can also be used to protect non-automated actions. For example, when a call center expert contacts a user to clarify or confirm a sensitive operation. + + This API is used by an application to get information about a mobile line latest SIM swap date. It can be easily integrated and used through this secured API and allows SPs (Service Provider) to get this information an easy & secured way. The API provides management of 2 endpoints answering 2 distinct questions: + + * When did the last SIM swap occur? + * Has a SIM swap occurred during last n hours? + + # Relevant terms and definitions + + **SIM swap**: + A SIM swap is a process in which a user's mobile phone number (MSISDN) is associated with a new SIM card (IMSI). This is typically done by contacting the user's mobile service provider and requesting a new SIM card for various reasons, such as a lost or damaged SIM card or upgrading to a new phone. + + SIM swap also happens during other actions like changing user's phone number, changing mobile service provider keeping user's mobile phone number or when activating a new SIM associated to the same phone number, known as multisim service. New subscription is considered as a SIM swap as well, the MSISDN which can be used by another person earlier, is associated with a SIM card it was not associated before. + + # API functionality + + The API provides 2 operations: + + - POST retrieve-date : Provides timestamp of latest SIM swap, if any, for a given phone number. + + - If no swap has been performed and the network operator supports unlimited SimSwap monitoring timeframe, the API will return the SIM activation date (the timestamp of the first time that the SIM connected to the network). + + - If the latest SIM swap date (or the activation date if no SIM swap) cannot be communicated due to local regulations (or MNO internal privacy policies) preventing the safekeeping of the information for longer than the stated period, a `null` value will be returned. Optionally, a `monitoredPeriod` could be provided to indicate monitored time frame (in days) supported by the MNO. In this case the response must be treated as "there were no sim swap events during 'monitoredPeriod'. Either the parameter is optional, it is recommended to support it in SimSwap implementations. + + - POST check: Checks if SIM swap has been performed during a past period (defined in the request with 'maxAge' attribute) for a given phone number. + + - Note: In the specification of the API the 'maxAge' could be between 1 hour to 2400 hours. If this delay is not managed due to the operator's own privacy threshold (which in theory would likely be linked to local regulations in the country) and a request is performed with a value inferior to 2400 but superior to operator policy, then, an error `400 OUT_OF_RANGE `is expected with an explicit message to explain the limitation like `Check monitor period could not exceed local regulations (30 days)`. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the provider of the application consuming the API and the operator's API exposure platform, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API. There is 2 ways to retrieve it depending on the authorization flow used: + - When the API is invoked using a two-legged access token, the phone number will be identified from the optional `phoneNumber` identifier, which therefore MUST be provided. + - When a three-legged access token is used however, this optional `phoneNumber` identifier MUST NOT be provided, as the phone number will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + + - If the phoneNumber cannot be identified from the access token and the optional `phoneNumber` identifier is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the phoneNumber can be identified from the access token and the optional `phoneNumber` identifier is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device is identified by these two methods, as the server is unable to make this comparison. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + [GSMA Mobile Connect Account Takeover Protection specification](https://www.gsma.com/identity/wp-content/uploads/2022/12/IDY.24-Mobile-Connect-Account-Takeover-Protection-Definition-and-Technical-Requirements-v2.0.pdf) was used as source of input for this API. For more about Mobile Connect, please see [Mobile Connect website](https://mobileconnect.io/). + + (FAQs will be added in a later version of the documentation) + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: wip + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/SimSwap +servers: + - url: "{apiRoot}/sim-swap/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` +paths: + /retrieve-date: + post: + security: + - openId: + - sim-swap:retrieve-date + - openId: + - sim-swap + tags: + - Retrieve SIM swap date + summary: Retrieve SIM swap date + description: Get timestamp of last SIM swap event for a mobile user account provided with phone number. + operationId: retrieveSimSwapDate + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a SIM swap date request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateSimSwapDate" + examples: + RETRIEVE_3LEGS: + $ref: "#/components/examples/RETRIEVE_3LEGS" + RETRIEVE_2LEGS: + $ref: "#/components/examples/RETRIEVE_2LEGS" + + required: true + responses: + "200": + description: Contains information about SIM swap change + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/SimSwapInfo" + examples: + RETRIEVE_DATE: + $ref: "#/components/examples/RETRIEVE_DATE" + RETRIEVE_MONITORED_PERIOD: + $ref: "#/components/examples/RETRIEVE_MONITORED_PERIOD" + RETRIEVE_MONITORED_NULL: + $ref: "#/components/examples/RETRIEVE_MONITORED_NULL" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + /check: + post: + security: + - openId: + - sim-swap:check + - openId: + - sim-swap + tags: + - Check SIM swap + summary: Check SIM swap + description: Check if SIM swap has been performed during a past period + operationId: checkSimSwap + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + description: | + Create a check SIM swap request for a phone number. + content: + application/json: + schema: + $ref: "#/components/schemas/CreateCheckSimSwap" + examples: + CHECK_3LEGS: + $ref: "#/components/examples/CHECK_3LEGS" + CHECK_2LEGS: + $ref: "#/components/examples/CHECK_2LEGS" + required: true + responses: + "200": + description: Returns whether a SIM swap has been performed during a past period + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/CheckSimSwapInfo" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SimSwapInfo: + type: object + required: + - latestSimChange + properties: + latestSimChange: + type: string + format: date-time + description: Timestamp of latest SIM swap performed. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + nullable: true + example: "2023-07-03T14:27:08.312+02:00" + monitoredPeriod: + type: integer + description: Timeframe in days for SIM card change supervision for the phone number. It could be valued in the response if the latest SIM swap occurred before this monitored period. + example: 120 + CheckSimSwapInfo: + type: object + required: + - swapped + properties: + swapped: + type: boolean + description: Indicates whether the SIM card has been swapped during the + period within the provided age. + PhoneNumber: + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: '+346661113334' + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + CreateCheckSimSwap: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + maxAge: + type: integer + example: 240 + description: | + Period in hours to be checked for SIM swap. + format: int32 + minimum: 1 + maximum: 2400 + default: 240 + CreateSimSwapDate: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: phone number is not included in the request (in case of 2-legged) or the phone number identification cannot be derived from access token (in 3-legged) + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Rejected due to exceeding a business quota limit. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rejected due to request rate limit overpassed. + examples: + RETRIEVE_DATE: + summary: Lastest SIM swap date is send back + value: + latestSimChange: 2024-09-18T07:37:53.471829447Z + RETRIEVE_MONITORED_NULL: + summary: Only null value is retrieved + value: + latestSimChange: null + RETRIEVE_MONITORED_PERIOD: + summary: null is send back for the date but a monitoredPeriod is provided + value: + latestSimChange: null + monitoredPeriod: 120 + CHECK_2LEGS: + summary: Check request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + maxAge: 120 + CHECK_3LEGS: + summary: Check request with 3-legged access tokens + value: + maxAge: 120 + RETRIEVE_2LEGS: + summary: Retrieve request without 3-legged access tokens + value: + phoneNumber: "+346661113334" + RETRIEVE_3LEGS: + summary: Retrieve request with 3-legged access tokens + value: + {} diff --git a/original/SimSwap/documentation/API_documentation/README.MD b/original/SimSwap/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..e69de29bb2d1d6434b8b29ae775ad8c2e48c5391 diff --git a/original/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story.md b/original/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..57c7e192ca39763143411382a3fa76ede9556871 --- /dev/null +++ b/original/SimSwap/documentation/API_documentation/SIM-Swap_check_User_Story.md @@ -0,0 +1,11 @@ +# SIM Swap Check API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to check if a SIM swap has occurred within a specified period for a user's mobile number so that I can enhance security measures against account takeover fraud. | +| ***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                                        **Scope:**
                                                                        - Checks if a SIM swap has occurred within a specified period for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                        1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                                        2. The ASP:BusinessManager has successfully subscribed to the SIM Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                                                        3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                                                        4. The ASP:User performs an authorization request to CSP
                                                                        5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                                        6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the SIM Swap API, providing the phone number and the desired period to check for SIM swaps. This request could be done via (or not) the Channel Partner.
                                                                          **Ends when:** The CSP's SIM Swap server responds indicating whether a SIM Swap has been performed within the specified period. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the SIM based on the SIM Swap information. | +| ***Exceptions*** | Several exceptions might occur during the SIM Swap API operations
                                                                          - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                                                          - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).| \ No newline at end of file diff --git a/original/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md b/original/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..47e2a6fef9cc442fb06bed26ef545b34590be517 --- /dev/null +++ b/original/SimSwap/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md @@ -0,0 +1,11 @@ +# SIM Swap Retrieve API User Story + + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an enterprise application developer, I want to verify the last SIM swap date for a user's mobile number so that I can enhance security measures against account takeover fraud. | +|***Actors and Scope*** | **Actors:** Application service provider (ASP), ASP:User, ASP: BusinessManager, ASP:Administrator, Channel Partner, End-User, Communication Service Provider (CSP).
                                                                          **Scope:**
                                                                          - Retrieves the timestamp of the last SIM swap event for a given phone number. | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                          1. The ASP:BusinessManager and ASP:Administrator have been onboarded to the CSP's API platform via (or not) a Channel Partner.
                                                                          2. The ASP:BusinessManager has successfully subscribed to the SIM Swap API product from the CSP's product catalog via (or not) a Channel Partner.
                                                                          3. The ASP:Administrator has onboarded the ASP:User to the platform.
                                                                          4. The ASP:User performs an authorization request to CSP
                                                                          5. The CSP checks access & End-User approval then provide access token to the ASP:User
                                                                          6. The ASP:User get the access token, via (or not) the Channel Partner, allowing a secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The ASP:User makes a POST request via the SIM Swap API, including the phone number provided by the End-User in the ASP:User.
                                                                            **Ends when:** The CSP's SIM Swap server responds with the timestamp of the last SIM swap event, or the SIM activation date if no swap has occurred. | +| ***Post-conditions*** | The ASP:User could continue offering its service to the End-User with the confirmation of the validity of the SIM based on the SIM Swap information. | +| ***Exceptions*** | Several exceptions might occur during the SIM Swap API operations
                                                                            - Unauthorized: Not valid credentials (e.g., use of already expired access token).
                                                                            - Invalid input: Not valid input data to invoke operation (e.g., improperly formatted phone number).
                                                                            - Not able to provide: Legal restrictions or data retention policies preventing the retrieval of the requested information.| diff --git a/original/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist.md b/original/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..e092a48c13d61ecbf6aba21e2aaf3c0eb041b3e2 --- /dev/null +++ b/original/SimSwap/documentation/API_documentation/sim-swap-API-Readiness-Checklist.md @@ -0,0 +1,31 @@ +# API Readiness Checklist + +Checklist for sim-swap 2.1.0 in r3.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                            public | stable
                                                                            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](code/API_definitions/sim-swap.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/API_definitions/sim-swap.yaml) | +| 6 | User stories | O | O | O | M | Y | [check](/documentation/API_documentation/SIM-Swap_check_User_Story.md) [retrieve](/documentation/API_documentation/SIM-Swap_retrieve_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [check](/code/Test_definitions/sim-swap-checkSimSwap.feature) [retrieve](/code/Test_definitions/sim-swap-retrieveSimSwapDate.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [check](/code/Test_definitions/sim-swap-checkSimSwap.feature) [retrieve](/code/Test_definitions/sim-swap-retrieveSimSwapDate.feature) | +| 9 | Test result statement | O | O | O | M | tbd | see [issue #233](https://github.com/camaraproject/SimSwap/issues/233) | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | [relative link](https://www.open-gateway.gsma.com/operators-map) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IAPWB) | + +(*) If you encounter issues with the provided test files (.feature), please create an issue in the API Sub-Project to signal these issues so they can be fixed in a patch release. + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist.md b/original/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..145209e3ec4d97c4019f7a8a73687afadb558d0b --- /dev/null +++ b/original/SimSwap/documentation/API_documentation/sim-swap-subscriptions-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for sim-swap-subscriptions 0.3.0 in r3.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                            public | stable
                                                                            public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](code/API_definitions/sim-swap-subscriptions.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Embedded documentation into API spec - [link](/code/API_definitions/sim-swap.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/sim-swap-subscriptions.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/IAPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..c287b83356ba212a848b7d7507652e60ee7f1e55 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2022_Week46_syncCalls.md @@ -0,0 +1,54 @@ +#Participants + + +**Week 46** + +15 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Garreth Williams|GSMA| +|2|Mona Mokhber|Telefonica| +|3|José Luis Urien Pinedo|Telefonica| +|4|Ludovic Robert|Orange| +|5|Dawid Wróblewski|DT| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + + +#Agenda +1. progress of work +2. backlog items (grooming) +3. priorities for items +4. AOB + +#MoM + +1. Dawid Wroblewski (DW) presented information about Mobile Connect API services that are commercially available and CAMARA is willing to adopt them: + 1. **Mobile Connect Verified MSISDN** as *Number Verify* + 2. **Mobile Connect Authenticate with SMS OTP** as *Number Verify SMS 2FA* + 3. **Mobile Connect Account Takeover Protection** as *SimSwap* + +2. DW mentioned about off-line discussion between Orange and DT regarding Sim Swap API: + 1. there are two different ideas how to handle API result + - sim swap timestamp + - boolean (Yes/No) i a given period (checks if sim swap was present in e.g. last 24h) + + 2. additionally, there are two different API design patterns on a table: + - API logic triggered by a dedicated "scope" value inside OAUTH2.0 Token Request - Mobile Connect like + - API logic triggered by a dedicated URL path + 3. DW took action to rise an issue inside Commonalities Working Group to discuss this topic and shape the final design of CAMARA APIs + + [Issue #105](https://github.com/camaraproject/WorkingGroups/issues/105) + +3. Maria Virtudes Briz Ruiz (MVBR) mentioned that Telefonica (TEF) has sim swap API commercially available based on Mobile Connect API. Addition that TEF wants to make is to expose additional sim Swap flavour - boolean. +4. Toshi Wakayama (TW) asked if it is mandatory to deploy whole Mobile Connect platform to serve Mobile Connect services - DW response that it is not required. Mobile Connect defines the way that APIs are consumed nortbound (by developer/SP), but gives freedom to MNO how it is depoyed internaly (only gives some hints/recommendations about how to handle processes). +5. DW claimed that Number Verify service cannot be handled by a single endpoint - this requires a dedicated flow due to the fact that MSISDN discovery is handled by MNOs in a varioius ways, e.g. Header Enrichment, Token Servers, Dedicated OAUTH platforms, EAP-AKA, etc. +6. Participants agree that it is critical to have a common approach to API design pattern to progress with firther API services design. diff --git a/original/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..eecfcad02437ef42adfe5390c343c1fdd776c714 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2022_Week50_syncCalls.md @@ -0,0 +1,99 @@ +# Week 50 meeting + +## Participants + +13 December 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jens Pöschl|DT| +|3|Andrzej Ochocki|DT| +|4|Ludovic ROBERT|Orange| +|5|Patrice CONIL|Orange| +|6|MARIA VIRTUDES BRIZ RUIZ|Telefonica| +|7|MONA MOKHBER|Telefonica| +|8|José Luis Urien Pinedo|Telefonica| +|9|GLYN POVAH|Telefonica| +|10|Adri Loloci|Vodafone| +|11|Mus Dumenci|Hutchison| +|12|Fabrizio Moggio|TIM Italy| +|13|Helene Vigue|GSMA| +|14|Toyeeb Rehman|GSMA| +|15|Mark Cornall|GSMA| + +17 November 2022: +|No|Name|Company| +|:---:|:---|:---:| +|1|Maria Virtudes Briz Ruiz|Telefonica| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|Harin Honesyandi Parandika|XL Indonesia| +|5|Heny Setywan|XL Indonesia| +|6|Dawid Wróblewski|DT| + +## Agenda + +1. Current activities status & introduction to guests +2. presenting Mobile Identity APIs +3. Telefonica presentation (10min) +4. Vodafone presentation (10min) +5. DT presentation (10min) +6. Q&A session + +## MoM + +1. Dawid Wroblewski (DW) presented the status of current activities inside GitHub: +### **simSwap API** + #### Recommendation: + >Enable simSwap API via OAUTH2.0 flows: + - OAUTH2.0 code flow/OpenID Connect + - OAUTH2.0 Client Credentials grant + + >Enable simSwap API flavors: + - based on dedicated endpoint (Orange + TEF proposal) + - based on MC ATP API description + +MNOs continue work and aiming to deliver APIs by the end of this week. + + ------- + + >following items were not presented during meeting, although sharing status and recommendations + +### NumberVerify SMS 2FA + +#### Recommendation: + + **Rename API family** to create more self-explanatory name. + Proposal: **OTP Verification API** + Supperted by: DT, Orange +
                                                                            Current shape of this service has nothing to do with Number Verify, therefore naming is misleading. It looks that it is more related with messaging APIs rather than identity APIs. It is highly appreciated that **Telefonica** representatives takes the lead in shaping this API.
                                                                            + +### NumberVerify + +#### Recommendation: + +**Keep CAMARA flow consistent with Number Verify / Mobile Connect Verified MSISDN service design.** +This particular service has to be considered by MNO community as a whole service flow, starting from /authorize, ending with resource call. Otherwise, software developers might get confused due t ovarious ways of handling device authentication. Number Verify service hides this complexity behind ***/authorize*** endpoint. Device authentication is handled by MNOs in various ways, e.g. by using redirects to dedicated device indentification services, Header Enrichment, private IP based device detection, public IP+port based device detection. Protected resources, either it is a dedicated endpoint (**/number_verify**) or a common (**/userinfo**) should be protected with OAUTH2.0/OpenID Connect **Authorization Code** flow (three-legged-token). This helps to assure that only authorized clients are capable of consuming protected resources. + +----- + +>meetng covered AoB topics that orbited API design & CAMARA goals topics. + +## AoB + +1. Vodafone (Adri) & Hutchison (Mus) requested information of CAMARA's goals. +2. Vodafone supports simSwap over MC ATP with Client Credentials. +3. GSMA (Mark) provided information about CAMARA & Openverse initiatives. + - vision: Enable 5G APIs + - API federtion + - ease of use for developers +4. Hutchison (Mus) shared lessons learnt from delivering Identity APIs countries where Hutchison operates. +5. Deutsche Telekom (Jens) requested information about the ideas for CAMARA Business Model. +6. Vodafone states that MNOs should focus on customers, trying to identify the problem, aligning on desired attributes, functional and non-funcional features, + +## APs + +1. GSMA to provide information about Openverse stakeholders (Done - Helen provided list to Vodafone and Hutchoison). +2. simSwap - work with 2 yaml files with API description +3. Number Verify - continue work based on MC Verified MSISDN specification, considering whole service flow. +4. Number Verify SMS 2FA - change the name of API and continue work to deliver OTP validation API. \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4639992f7412b80dbb4481c6e0866f1977c2e961 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week20_syncCalls.md @@ -0,0 +1,42 @@ +# Week 20 meeting + +## Participants + +18th May 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +- general discussion about API status + +### Sim Swap API + +- no updates + +### NumberVerify + +- no updates + +### OTP Validation + +- no updates + +----- + +## AoB + +- no AoB + +## APs + +- no APs \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4bc16d0e1e7c45a108ac368ad066ec354b9d5266 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week22_syncCalls.md @@ -0,0 +1,42 @@ +# Week 22 meeting + +## Participants + +1st June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Toshi Wakayama|KDDI| +|5|Shuting Qing|Huawei| +|6|Mohammad Sahid Khan|Etisalat| +|7|Prashant Sidana|Etisalat| +|8|Cormac Hegarty A|Ericsson| +|9|Gregory Liokumovich|Ericsson| +|10|Gareth Williams|GSMA| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +### NumberVerify + +### OTP Validation + +- discussion about Etisalat proposal Issue#27 + +----- + +## AoB + +- no AoB + +## APs + +1. Continue discussion inside Github \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..781b58c433f89b8f85172128ff1fe8160a66058f --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week24_syncCalls.md @@ -0,0 +1,55 @@ +# Week 24 meeting + +## Participants + +15th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|Klaus Reifenrath|Vodafone| +|4|Sönke Peters|Vodafone| +|5|Nevin Aquinas|Vodafone| +|6|Wolfgang Arendt|Vodafone| +|7|Ludovic ROBERT|Orange| +|8|Toshi (Toshiyasu) Wakayama|KDDI| +|9|Gautam Hazari|Sekura| +|10|Mohammad Sahid Khan|Etisalat| +|11|Prashant Sidana|Etisalat| +|12|Cormac Hegarty A|Ericsson| +|13|Gregory Liokumovich|Ericsson| +|14|Ashwin Nabil Careem|IBEM| +|15|Sajith Nedunmullage|IBEM| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- discussed error code for a scenario when MSISDN cannot be handled by MNO => general code message was suggested and placed inside PR +- Timezone discussion => AP to move it to commonalities +- discussion about how to handle Mobile Connect APIs => 3 scenarios came out from discussion: + 1. create a dedicated sub-project for Mobile Connect APIs inside Camara + 2. create a dedicated branch & tag inside existing repositories + 3. create a reference to Mobile Connect APIs inside Camara API description and archive MC flavor => AP to place these inside Issue#200 inside Commonalities WG + +### NumberVerification +- merged PR, which delivers details/enhancements for Camara NumberVerify API decsriptin (yaml) +- sequence diagram presents high level flow. Additional description regarding *Network Authentication* might be required. +- Discussion around Access Token - for NumberVerify it is impossible to use an Access Token from other APIs, e.g. QoD, as NumberVerification API requires building an MNO context beteween client and MNO, so Access Token is unique for this scenario + +### OTP Validation +- Etisalat (Mohammad) described use cases for *message_id* parameter + +----- + +## AoB + +## APs +1. Take discussion about time format to Commonalities WG => @bigludo7 +2. Prepare scenarios for Mobile Connect APIs handling for a decission to move forward => @DT-DawidWroblewski +3. Etisalat to deliver use case description for *message_id* and onboarding procedure and place it in GitHub. Afterwards group shall decide how to progress with this change inside OTPValidationAPI repo diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..351a58feb66e00d227170793ed710eea46a64e99 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week26_syncCalls.md @@ -0,0 +1,47 @@ +# Week 26 meeting + +## Participants + +29th June 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|MONA MOKHBER|Telefonica| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Klaus Reifenrath|Vodafone| +|5|Ludovic ROBERT|Orange| +|6|Toshi (Toshiyasu) Wakayama|KDDI| +|7|Cormac Hegarty A|Ericsson| +|8|Gregory Liokumovich|Ericsson| +|9|Sajith Nedunmullage|IBEM| +|10|Gareth Williams|GSMA| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- disussion to introduce new idea to SIM swap repo, to deliver sim swap event as a stream. This idea shall be discussed further. + +### NumberVerification +- merged PR regarding text of API description +- discussion about issue #33 - versioning + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- @bigludo7 gave a briefing from OPG/OPAG meeting in London +- + +## APs +1. AP @DT-DawidWroblewski => prepare a text that shall be used as a reference to Mobile Connect standard within Camara APIs, according to discussion inside #200. @monamok suggested to have 2 PRs for this activity: + 1. for deleting two flavors and leaving one (CAMARA) for avoiding confusion inside Camara repositories + 2. for adding reference text +2. AP @DT-DawidWroblewski create a release for NumberVerify API from commit "db1665" \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..e70e969106c2376dc89688ffc74a63d98838d234 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week2_syncCalls.md @@ -0,0 +1,56 @@ +# Week 2 meeting + +## Participants + +10 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Gareth Williams|GSMA| +|3|Ludovic ROBERT|Orange| +|4|Patrice CONIL|Orange| +|5|MONA MOKHBER|Telefonica| + + +12 January 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Jung Yun-sun (Serena)|SK Telecom| +|3|Toshi Wakayama|KDDI| +|4|MONA MOKHBER|Telefonica| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap API + +- CAMARA & MC APIs yaml files delvered + +### NumberVerify + +- CAMARA & MC APIs yaml files delvered + +### OTP Validation + +- CAMARA yaml available + +- work on track + +----- + +## AoB + +1. Dawid from DT explained differences between MC APIs & CAMARA APIs upon KDDI request (Toshi) + +## APs + +1. Provide a proper naming for md files inside API documentation +2. Merge PR inside OTP Validation. +3. Describe SP onboarding flow with *Use Case Declaration* that implies Sim Swap confguration. Provide this inside API documentation. Make a new PR for this. +4. For All APIs: provide description inside *readme.md* of having 2 yaml files (history, results of discussions). +5. Version control issue - tackle this inside *Commonalities WG*. diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..dbaf949d9342dc586b323020dd24d58af93a054c --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week32_syncCalls.md @@ -0,0 +1,35 @@ +# Week 32 meeting + +## Participants + +10th August 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Toshi (Toshiyasu) Wakayama|KDDI| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +- working on "cleaning repo" PR + +### NumberVerification +- working on "cleaning repo" PR + +### OTP Validation +- discussion about having 3-legged-token within the API flow + +----- + +## AoB +- no AoB (vacation) +- + +## APs +1. no additional APs (vacation) \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71e4117b347508f92e11b975698fad270626d34e --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week36_syncCalls.md @@ -0,0 +1,53 @@ +# Week 36 meeting + +## Participants + +9th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Prashant Sidana|Etisalat| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. Alexander Boraczyński requested to have information about differences between Mobile Connect & CAMARA versions of SimSwap API to have visibility on changes that have to be performed on local systems to implement CAMARA API flavour, as Mobile Connect APIs are currently commercially served on the German market (Local Champion activity). +2. Notification/subscription concept to be introduced as an issue that will work out the PR that brings new API in SimSwap family (new yaml file and API description). + - @bigludo7 shall create an issue to continue the discussion about this topic. + - @DT-DawidWroblewski suggested using [Mobile Connect IDY.02 specification](https://www.gsma.com/identity/wp-content/uploads/2022/11/IDY.02-v2.0.pdf) as a starting point to this discussion, as it implements CIBA with polling and notification functions. + - @gregory1g mentioned that specific MSISDN lifecycle events, like MSISDN port-out from CSP should be taken into consideration while designing notification services - cancelling subscription on such an event +3. @psidana1983 asked about the Camara compliance topic: What if MNO decides to implement only a single endpoint from the API description? @bigludo7 explained that it is fine to do so, although the other endpoint should get proper handling and give an error response (e.g. API unavailable) + +### NumberVerification +1. NumberVerification API repo requires consolidation - @fernandopradocabrillo will create a PR with changes +2. @ecormac mentioned inconsistency in security/auth schemes in API definition OAUTH2.0 Authorization Code & OpenID Connect are used across the document - this should be fixed. +3. @ecormac asked about the condition of NumberVerification API and if it is stable enough for developers to use. @DT-DawidWroblewski confirmed that resource definition is stable and can be used for resource exposure towards developers. However, today it is challenging to have a common service description towards developers due to multiple ways of doing Network Authentication across the MNO landscape. + +### OTP Validation +1. Stable version - no issues or pending PRs + +----- + +## AoB + + +## APs +1. @fernandopradocabrillo Updates PR #52: + - Update version number + - undelete oauth2clientCredentials +2. @fernandopradocabrillo creates a dedicated PR for changes to security in yaml, according to commonalities work +3. @fernandopradocabrillo creates a PR for NumberVerification API that consolidates API information into yaml file and syncs with commonalities (similar to PR from SimSwap API) +4. @ecormac creates an issue with the authentication description issue inside the NumberVerification description \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ef5342ee522e0fba8d0eb487ef07eabb7eeb0dec --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week38_syncCalls.md @@ -0,0 +1,50 @@ +# Week 38 meeting + +## Participants + +21th September 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|Sönke Peters|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Udaka Kappagoda|Axiata Digital Labs| +|9|Gregory Liokumovich|Ericsson| +|10|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion +2. new API description that use notifications scheme +3. UTC time - next API modification should include this change +### NumberVerification +1. security scheme discussion + +- OpenID Connect vs. OAUTH2.0 authorization code grant flow +- should auth server deliver id_tokens? +- how scopes impacts id_token creation +### OTP Validation +- no updates + +----- + +## AoB + +1. Security scheme discussion +- discussion about country/market differences with regards to security schemes in commercially available API solutions like Mobile Connect +- solution should be provided, that is based on buisiness/legal discussion stream + +## APs +1. Create a distinct yaml that describes notifications scheme \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ae2c49ba5cbbca3cfc4c0e9c8f2843d0f117ef11 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week40_syncCalls.md @@ -0,0 +1,65 @@ +# Week 38 meeting + +## Participants + +2nd October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Klaus Reifenrath|Vodafone| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|Toshi Wakayama|KDDI| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| + + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. security scheme discussion + +- OAUTH2.0 Client credentials security scheme should supported by SIM Swap API, as this solution that is currently serverd to customers within Mobile Connect API services suite. +- Commonalities WG delivered an elegant solution to discover security schemes, that are available +- changes has to be introduced to API description that gives developer information about what security schemes are supported -> AP + +2. API version + +- discussion about moving towards v0.8.0, that can be used to create a release + +3. API release + +- release version should be created upon merged PR + + +### NumberVerification +1. product naminig +2. updating scope values +3. network based authentication description +4. UML update +### OTP Validation +1. API version + +- it has been agreed to update API version to 0.8.0 and create release version + +----- + +## AoB + +1. security schemes discussion in Commonalities + +currently there is a strong recommendation from Commonalities WG to use three-legged-token flow for APIs that involves end-user resource. However, it is up to sub-project to specify details of each API security scheme. + +## APs +1. @DT-DawidWroblewski creates commit to @fernandopradocabrillo PR in SimSwap API sub-project, with addons: + 1. description in yaml about supported security schemes inside SimSwap API + 2. version 0.8.0 +2. @DT-DawidWroblewski creates SimSwap API release version based on v0.8.0 +3. @DT-DawidWroblewski updates OTPValidation API version to 0.8.0 +4. @DT-DawidWroblewski creates OTPValidation API release version based on v0.8.0 \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..71b83502cdd314d2723ed46f852e4e1e6cad899b --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week42_syncCalls.md @@ -0,0 +1,58 @@ +# Week 42 meeting + +## Participants + +19th October 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Sönke Peters|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toyeeb Rehman|GSMA| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. SimSwap Notification Subscription API + +- subscribing to SIM swap events might bring some new legal challenges - get feedback from marketing/legal about subscribing to End-User data resource events. -> AP +- Notification Subscription API requires different technical solutions on the MNO side. Therefore, it requires a feasibility study on the MNO side + +2. Discussion on the [Issue#16](https://github.com/camaraproject/SimSwap/issues/16) + +- An empty string value may be feasible, as it enables API to deliver 200 OK in an event where no SIM change occurred +- null may be an option +- SIM card activation date may be an option, although it should be limited, i.e. it makes sense when it is limited by period (e.g. when the activation date is older than 30 days it does not make sense to return it) + +3. Test cases discussion +- @trehman-gsma introduced test cases for Camara SIM Swap API +- an issue shall follow to discuss this topic -> AP +- release version should be created upon merged PR + +### NumberVerification +1. Discussion on the Issue [#61](https://github.com/camaraproject/NumberVerification/issues/61) and changes introduced in the [PR#60](https://github.com/camaraproject/NumberVerification/pull/60) +- changes introduced by TEF point to usage of OAUTH2.0 Authorization Code grant, therefore security scheme has to be updated, as it is not OpenID Connect (that creates id_token & access_token) +- there should be a general rule describing access_token - should it be in the form of JWT? What claims should it contain? Once TEF delivers a statement about changes introduced, a discussion should follow inside Commonalities WG + + +### OTP Validation +1. release version [v0.5.0](https://github.com/camaraproject/OTPvalidationAPI/releases/tag/v0.5.0) created + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski gets initial feedback from Telekom about subscribing to end-user data resource events +2. @trehman-gsma creates an issue to discuss test cases for Camara SIM Swap API \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..a94f8f5d6bac7f2509c642fdbb9d8cc87ba66ab5 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week44_syncCalls.md @@ -0,0 +1,63 @@ +# Week 44 meeting + +## Participants + +2nd November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Alexander Boraczynski|Vodafone| +|3|Klaus Reifenrath|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Toshi Wakayama|KDDI| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. activation date discussion + +> Problem: should it be considered as a sim swap event? + +- makes sense for a multi-sim scenario, when the new sim is activated +- delivering a flag, that informs about using the activation date is an option, although adding new keys in the response body triggers work with Data Privacy, as this would be a new attribute returned in the API response +- this can be country-specific information, therefore might require additional description (inside yaml) +- AP @DT-DawidWroblewski creates a dedicated issue for this problem +2. value on "no event" scenario +- returning "error" should not be considered a good solution, as CSP performs a sim swap check + +> Decision - use "null" value on an event of no sim change, delivered as a value + +2. Notification subscription PR +- work ongoing +- callback URL: should it be a part of developer onboarding? + +### NumberVerification +1. Product naming +2. OpenID Connect vs OAUTH2.0 +- OpenID Connect stays as a Camara preferred security scheme +- it means that */token* response contains tokens: **id_token** & **access_token** +- there is concern about the content of **id token sub value** - requires further discussion +- AP @fernandopradocabrillo - create a PR to fix the description in yaml + + +### OTP Validation + +- no updates + +----- + +## AoB + +1. No AoB + +## APs +1. @DT-DawidWroblewski create a dedicated issue for a problem: should activation_date be considered as a sim swap event? +2. @fernandopradocabrillo - create a PR to fix description in yaml regarding access_token \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..835b03e3b1b3acb6e8486f8860614cdecbfd2878 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week46_syncCalls.md @@ -0,0 +1,48 @@ +# Week 46 meeting + +## Participants + +16th November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Klaus Reifenrath|Vodafone| +|4|Sebastian Köller|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|ROBERT Ludovic|Orange| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. work towards new release, that is based on v0.5.0 +2. new error message: **403** - PR awaits approval +3. Test cases - make an offline session between TEF & GSMA + +### NumberVerification +1. release version requires fix - accoplish tasks to next version and make a cleanup +2. phone number format discussion - wait for commonalities to provide information what format should be used + +### OTP Validation + + +## AoB + +- discussion about what what API requires to achieve **1.0.0.** + - fixed scopes + - commonalities guidelines + - create release candidate +- discussion about **Camara Winter 2024 release** +- Slack communication channel for informal communication + + +## APs +- @DT-DawidWroblewski review PRs (403 & notification) \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..ed8d2c7ae64f5ceb222a5b2d843bdcafb15268f8 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week48_syncCalls.md @@ -0,0 +1,60 @@ +# Week 48 meeting + +## Participants + +30th November 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Sönke Peters|Vodafone| +|3|Sebastian Köller|Vodafone| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Foo Ming Hui|Singtel| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discusson about sub-project/API name. + + Sugesstion that simSwap might be misleading, as for the audience it is explicit event, when subscriber makes a change of a SIM card. + + In general the scope of API is fine - it delivers a date of a last MSISDN and IMSI pairing, although it would be better to place additional use cases and sim swap scenarios in API description. + +2. X-correlator + + X-correlator header should be a part of all API operators. + +3. Test cases + + waiting for commonalities WG to deliver guidelines about test cases + +### NumberVerification + +1. Discussion about "eligibility check" before triggering Number Verification flow. +2. @DT-DawidWroblewski mentioned about activity in GSMA Authorization Server Authenticator Capabilities (ASAC) group, where community discuss about eligibility check and seamless authenticator capabilities. + +[Link to join](https://myaccess.microsoft.com/%40MemberGateway.onmicrosoft.com#/access-packages/6658a7c4-7b25-4731-a3bc-b9bd7af7d2b1) +[Link to group](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + +### OTP Validation +- no updates + +----- + +## AoB + +- no AoB + +## APs +* AP1 @gregory1g creates a PR to simSwap API that adds new description and use cases for simSwap event +* AP2 @fernandopradocabrillo creates a PR to add x-correlator to simSwap API +* \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..0ada220a2eb0a94897d6cae29d0987574518d276 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2023_Week50_syncCalls.md @@ -0,0 +1,60 @@ +# Week 50 meeting + +## Participants + +14 December 2023: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|ROBERT Ludovic|Orange| +|3|Toyeeb Rehman|GSMA| +|4|Gregory Liokumovich|Ericsson| +|5|Cormac Hegarty A|Ericsson| + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about returned objects, while API cannot provide a legitimate response + * if simSwap date is unavailable and service completed runtime, API should return object back to developer stating this fact + * current API design enables followng return options: + - ${date-time} + - null + - empty response + * conclusion is that it is up to business side to decide what should be returned +2. Test cases + * waiting for Commonalities WG guidelines + +### NumberVerification +1. Discussion about phone number format + * phone number pattern revieled in QoD sub-project + * discussion has been taken over to commonalities + * awaiting for commonalities guideline (@bigludo7 shares a link to discussion) + * check with +2. ad + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. Further assessment has to be performed to check if API definition follows commonalities guidelines with regards to status codes & messages + +## AoB + +1. OAS Linting + * check if simSwap, NumberVerification, OTPValidation projects can follow OAS linting + * topic triggered in [NumberVerificatio issue #75](https://github.com/camaraproject/NumberVerification/issues/75) +2. CSP definition + * sub-projects has to follow a common Camara glossary + * currently readers might experience confusion, when checking acronyms used in Camara, e.g. CSP can be defined as Communications Service Provider, but also as Cloud Service Provider +3. Discussion about Camara OIDC Profile, that is planned to be designed in 2024 + * should add more clarity to AuthN/AuthZ concept + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @trehman-gsma - adds a comment about conclusion from meeting inside [#16](https://github.com/camaraproject/SimSwap/issues/16) diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..2e87b4b18e751b1dfca19d0ccbff58516a21703b --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week10_syncCalls.md @@ -0,0 +1,45 @@ +# Week 10 meeting + +## Participants + +7 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. ICM (Axel Nennker) asked if simSwap API could be a candidate to specify e2e CIBA flow, based on upcoming Camara profile. +2. Closing issues: + * [#84](https://github.com/camaraproject/SimSwap/issues/84) +3. + +### NumberVerification +1. Disussion about "state of the market" + * Camara Number Verification vs Mobile Connect Verified MSISDN specs - due to the fact that Camara is a new solution available on a market it requires customers to get familiar with it. Mobile Connect APIs are available for some time now with customers consuming these APIs on commercial basis. + +### OTP Validation +1. Closing issues + * [#42](https://github.com/camaraproject/OTPvalidationAPI/issues/42) + +## AoB +1. @DT-DawidWroblewski is leaving simSwap, NumberVerification and OTPVerification API community leader role. Due to this change community has been requested to find a substitute. + +## APs +1. @DT-DawidWroblewski creates an issue to discuss how simSwap API description can incorporate CIBA flow based on Camara Profile (work in progress) \ No newline at end of file diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..4d21478b982bd60ae559d9aa4e6398cf0949b7ff --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week12_syncCalls.md @@ -0,0 +1,56 @@ +# Week 12 meeting + +## Participants + +21 March 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Cormac Hegarty A|Ericsson| +|7|Toshi Wakayama|KDDI| +|8|Alex|IPification| +|9|Parichaya Shrivastava|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Alex from IPFication mentioned about Number Recycle product that can enhance existing simSwap API family + * there was an ask to add this idea to Camara API backlog +2. Community discussed [PR#97](https://github.com/camaraproject/SimSwap/pull/94) + * changes are fixing issues [#96](https://github.com/camaraproject/SimSwap/issues/96) & [#16](https://github.com/camaraproject/SimSwap/issues/166) + * community decided to approve this PR +3. PRs regarding *testing* are awaiting resolution from [Commonalities WG](https://github.com/camaraproject/Commonalities/issues/94) + +### NumberVerification +1. Discussion on [Issue #86](https://github.com/camaraproject/NumberVerification/issues/86) + * @DT-DawidWroblewski mentioned about work that is currently concluded at GSMA Authorization Server Authenticator Capabilities Group, where new specification is in formal GSMA approval process. ETA - April 2024. + * [Link to Member Gateway](https://membergateway.sharepoint.com/sites/wg-ISAG-ASACG) + * it was suggested to move this issue to a discussion at [Identity&Consent Management group](https://github.com/camaraproject/IdentityAndConsentManagement) level +2. Number Verification API community input to [OIDC profile discussion](https://github.com/camaraproject/IdentityAndConsentManagement/pull/121) + * Number Verification API has its own specifics that has to be considered inside Camara OIDC profile, like: + * * no need to pass any phone number as a *login_hint* inside authorization request + * * it must follow OIDC flow, where *network authentication* happens at MNO */authorize* endpoint + * * ID Token is a result of OIDC flow, although it does not bring any value to developer currenlty (this might change when Camara community desceibes ID Token & access token in a context of ODIC flow) + * it was suggested to pass our community feedback **when first document, that decsribes Camara OIDC profile, arrives** + +### OTP Validation +1. Closing issues + * [#41](https://github.com/camaraproject/OTPvalidationAPI/issues/41) -> @DT-DawidWroblewski creates a PR to fix a link to release version + +## AoB +1. meeting series created by @DT-DawidWroblewski shall be canceled => @bigludo7 shall create new series on a same basis, i.e. every 2 weeks at Thursday, 8:30 AM, CET +2. @bigludo7 shall mention about *open position* for **simSwap/NumberVerification/OTPValidationAPI** lead at Camara TSC +3. @DT-DawidWroblewski mentioned that Deutsche Telekom delegates a new person to join this community + +## APs diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..0d3113d9a121a5cfefa735d20a647e062a863fc2 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week2_syncCalls.md @@ -0,0 +1,58 @@ +# Week 2 meeting + +## Participants + +11 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Klaus Reifenrath|Vodafone| +|5|FERNANDO PRADO CABRILLO|Telefonica| +|6|JORGE GARCIA HOSPITAL|Telefonica| +|7|Gregory Liokumovich|Ericsson| +|8|Cormac Hegarty A|Ericsson| +|9|Foo Ming Hui|Singtel| +|10|Victor Javier Quiroga Reyes|madisonmk.com| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *wildcard* scope handling + * describe a way to handle wildcard scopes inside API description + * requires adding new scope inside yaml file +2. New release API planned after MWC 2024 +3. Issue [#84](https://github.com/camaraproject/SimSwap/issues/84) discussion + * good summary provided by @eric-murray + * awaiting resolution inside commonalities +4. API requires fixing with regards to "null" value + * *lastSimChange* attribute should be **REQUIRED** + +### NumberVerification +1. Linting rules + * align with @rartych +2. Number Verify flow with aggregator + * @mhfoo provides sample diagram + * provide a reference to OGW + +### OTP Validation + +1. Check if OAUTH2.0 Client Credentials flow (2-legged) is applicable in this API +2. Current design makes it challenging to identify MNO that has to serve this API, i.e. there is no MNO discover process (e.g. with a support of Telco Finder) in place +3. @ajamus is asked to join for a discussion + +## AoB + +N/A + +## APs +1. AP1 @DT-DawidWroblewski - creates a PR to simSwap api and makes lastSimChange attribute **REQUIRED** +2. AP2 @mhfoo - creates a sequence diagram diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..8231efe5770b6d7f1e29a80710342d8b0f24bf64 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week4_syncCalls.md @@ -0,0 +1,53 @@ +# Week 4 meeting + +## Participants + +25 January 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|Sönke Peters|Vodafone| +|4|Alexander Boraczynski|Vodafone| +|5|ROBERT Ludovic|Orange| +|6|FERNANDO PRADO CABRILLO|Telefonica| +|7|JORGE GARCIA HOSPITAL|Telefonica| +|8|Gregory Liokumovich|Ericsson| +|9|Cormac Hegarty A|Ericsson| +|10|Foo Ming Hui|Singtel| +|11|Surajj Jaggernath|Vodacom| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + +1. Discussion about *3-legged-flow* performance + * OIDC CIBA vs OAUTH2.0 Client Credentials + * end-user opt-out capability should be considered in overall discussion as well as Camara APIs characteristics, i.e. serving many developers and use cases + * flow optimisation is a must + +### NumberVerification +1. Discussion about Number Verify flow with aggregator provided by @mhfoo +2. Test Cases for Number Verification + +### OTP Validation + +N/A + +## AoB + +1. Onboarding APIs + * there is a discussion at OGW to use security schemes that works with specific use cases, e.g. Client Credentials works with AntiFraud use cases & banks as a service providers +2. Fine-tune error responses + * remove *409* + * ad error when phone *number is unknown* + +## APs +1. AP1 @DT-DawidWroblewski - checks the status of phone number format discussion with QoD sub-project leaders (@hdamker) +2. AP2 @bigludo7 - adds test cases for Number Verification - starting with an issue diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..8d16f89a41150a42bc40352511686d6a3c512f5f --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week6_syncCalls.md @@ -0,0 +1,42 @@ +# Week 6 meeting + +## Participants + +8 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|ROBERT Ludovic|Orange| +|4|FERNANDO PRADO CABRILLO|Telefonica| +|5|JORGE GARCIA HOSPITAL|Telefonica| +|6|Gregory Liokumovich|Ericsson| +|7|Cormac Hegarty A|Ericsson| +|8|Foo Ming Hui|Singtel| +|9|Surajj Jaggernath|Vodacom| +|10|Lazar Bulic|IPification| +|11|Alex|IPification| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap + + +### NumberVerification + + +### OTP Validation + + +## AoB + +* discussion about MWC 2024 +* add commits to sub-projects for next release + +## APs diff --git a/original/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls.md b/original/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls.md new file mode 100644 index 0000000000000000000000000000000000000000..04cbf65fda5ec2212f67cc70bf17681e3866c51a --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/2024_Week8_syncCalls.md @@ -0,0 +1,38 @@ +# Week 8 meeting + +## Participants + +22 February 2024: +|No|Name|Company| +|:---:|:---|:---:| +|1|Dawid Wróblewski **(organizer)**|DT| +|2|Huub Appelboom|KPN| +|3|JORGE GARCIA HOSPITAL|Telefonica| +|4|Alexander Boraczynski|Vodafone| +|5|Cormac Hegarty A|Ericsson| +|6|Gregory Liokumovich|Ericsson| +|7|Foo Ming Hui|Singtel| +|8|Alex|IPification| +|9|Ramesh Shanmugasundaram|spryfoxnetworks| + + +## Agenda + +1. Present information about actual work inside API repos. +2. AoB + +## MoM + +### Sim Swap +1. No updates - focus on MWC 2024 + +### NumberVerification +1. @sfnuser adds references to discussions around OIDC profiles. +2. No additional updates - focus on MWC 2024 + +### OTP Validation +1. No updates - focus on MWC 2024 + +## AoB + +## APs diff --git a/original/SimSwap/documentation/MeetingMinutes/README.MD b/original/SimSwap/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..85e60f516ddb3ab37e3e0de31bacfb31a60fda37 --- /dev/null +++ b/original/SimSwap/documentation/MeetingMinutes/README.MD @@ -0,0 +1,3 @@ +## RELEVANT INFORMATION + +Since April 4th 2024 WG meeting minutes are placed in [SIM Swap Wiki Confluence site](https://wiki.camaraproject.org/display/CAM/SIMSwap) diff --git a/original/SimpleEdgeDiscovery/README.md b/original/SimpleEdgeDiscovery/README.md new file mode 100644 index 0000000000000000000000000000000000000000..6a30367546956110fd2f23a5facb52b66f76a5ba --- /dev/null +++ b/original/SimpleEdgeDiscovery/README.md @@ -0,0 +1,51 @@ + + + + + + + + + +# SimpleEdgeDiscovery + +Incubating API Repository to evolve and maintain the definitions and documentation of SimpleEdgeDiscovery Service API(s) within the Sub Project [Edge Cloud](https://lf-camaraproject.atlassian.net/wiki/x/IwEpBQ) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/QwCbBQ) + +## Scope +* Service APIs for “SimpleEdgeDiscovery” (see APIBacklog.md) +* It provides the API Consumer with the ability to: + * Discover the closest edge cloud zone to a given device. + * NOTE: The scope of this API should be limited (at least at the first stage) to 4G and 5G. +* Describe, develop, document, and test the APIs +* Started: June 2022 (as part of [EdgeCloud](https://github.com/camaraproject/EdgeCloud/)) + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/SimpleEdgeDiscovery/releases/tag/r2.2) (Fall25), with the following API versions: + * **simple-edge-discovery v2.0.0** + [[YAML]](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/r2.2/code/API_definitions/simple-edge-discovery.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SimpleEdgeDiscovery/r2.2/code/API_definitions/simple-edge-discovery.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SimpleEdgeDiscovery/r2.2/code/API_definitions/simple-edge-discovery.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SimpleEdgeDiscovery/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SimpleEdgeDiscovery/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SimpleEdgeDiscovery/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings (as part of Edge Cloud Sub Project) + * [Registration/Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Schedule: Tuesdays 16h-17 CET, every two weeks. + * Minutes: Access [meeting minutes](https://wiki.camaraproject.org/display/CAM/EdgeCloud+Meeting+Minutes). +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project [https://lists.camaraproject.org/g/sp-edc](https://lists.camaraproject.org/g/sp-edc). + * A message to the community of this Sub Project can be sent using [sp-edc@lists.camaraproject.org](sp-edc@lists.camaraproject.org). diff --git a/original/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery.yaml b/original/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery.yaml new file mode 100644 index 0000000000000000000000000000000000000000..ff336b93cf526f041e590cafdf3af514cb40be04 --- /dev/null +++ b/original/SimpleEdgeDiscovery/code/API_definitions/simple-edge-discovery.yaml @@ -0,0 +1,708 @@ +--- +openapi: 3.0.3 +info: + title: Simple Edge Discovery + version: wip + x-camara-commonalities: 0.6 + description: | + # Find the closest Edge Cloud Zone + --- + # Summary + + The Simple Edge Discovery API returns the name of the closest operator Edge + Cloud Zone to a particular user device. + + # Purpose + Network operators may host multiple Edge Cloud Zones in a + given territory. Connecting your application to a server on the closest + Edge Cloud Zone means packets travel the shortest distance between + endpoints, typically resulting in the lowest round-trip latency. Note, the + physical (GPS) location of a user device is not a reliable way to determine + the closest Edge Cloud Zone, due to the way operator networks are routed - + so the operator will calculate the Edge Cloud Zone with the + _shortest network path_ to the network-attached device identified in the API + request. + + Once you have the name of the closest Edge Cloud Zone to the user device, + you may: + + * connect the application client on the user device to your application + server instance on that Edge Cloud Zone. Note: the IP address of that + application server instance is not part of the API response, so you will need + to map the edge cloud zone name to the server endpoint IP address you received + when you deployed the server via the cloud provider's API. + * or, if you have no instance on that Edge Cloud Zone, you may wish to + deploy one there using the cloud provider's APIs. + + Note: the provider of the Edge Cloud Zone may be an operator, or a cloud + provider working in partnership with the operator. + + # Usage + + The API may be called either by an application client hosted on a device + attached to the operator network (i.e. phone, tablet), or by a server. + + There is a single API endpoint: `/retrieve-closest-edge-cloud-zone`. + + To call this endpoint, the API consumer must first obtain a valid OAuth2 token + from the token endpoint, and pass it as an `Authorization` header in the API + request. + + # Identifying the device + + The API returns the closest Edge Cloud Zone to a given device, so that + device needs to be identifiable by the network. This can be achieved either + by passing one or more device identifiers in the request, or, from the + three-legged access token where implemented by the operator. + + ## Passing device identifier(s) in the request + At least one of the following device identifiers must be provided, unless + using a 3-legged access token (see next section): + - Phone number (i.e. MSISDN) + - Network Access Identifier assigned by the mobile network operator for the device + - IPv6 address + - IPv4 address + + + NOTE1: the network operator might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible across + different network operators. In this case the identifiers MUST belong to the + same device. + + NOTE2: for this Commonalities release, we are enforcing that the + `networkAccessIdentifier` is only part of the schema for future-proofing, and + CAMARA does not currently allow its use. After the CAMARA meta-release work + is concluded and the relevant issues are resolved, its use will need to be + explicitly documented in the guidelines. + + + ## Identifying the device from the access token + + This API requires the API consumer to identify a device as the subject of + the API as follows: + + - When the API is invoked using a two-legged access token, the subject will be + identified from the optional `device` object, which therefore MUST be provided. + - When a three-legged access token is used however, this optional identifier + MUST NOT be provided, as the subject will be uniquely identified from the access + token. + + This approach simplifies API usage for API consumers using a three-legged access + token to invoke the API by relying on the information that is associated with the + access token and was identified during the authentication process. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional `device` + object is not included in the request, then the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `device` + object is also included in the request, then the server will return an error with the + `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same device + is identified by these two methods, as the server is unable to make this comparison. + + # Responses + + ## Success + + A JSON object is returned containing an array with a single member object. + This contains identifiers for the closest Edge Cloud Zone. The HTTP status + code will be`200 OK`. An example response: + + ``` + [ + { + "edgeCloudZoneId": "4gt555-6457-7890-d4he-1dc79f44gb66", + "edgeCloudZoneName": "example zone name", + "edgeCloudProvider": "example zone provider" + } + ] + ``` + * `edgeCloudZoneId` is a UUID for the Edge Cloud Zone. + * `edgeCloudZoneName` is the common name of the closest Edge Cloud Zone to + the user device. + * `edgeCloudProvider` is the name of the operator or cloud provider of + the Edge Cloud Zone. + + ## Errors + + If the authentication token is not valid, a `401 UNAUTHENTICATED` error is + returned. + + If the mobile subscription parameters contain a formatting error, a `400 + INVALID_ARGUMENT` error is returned. + + If the mobile subscription cannot be identified from the provided + parameters, a `404 NOT_FOUND` error is returned. + + Any more general service failures will result in an error in the `5xx`range + with an explanation. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore + the API specification may not document some non-mandatory error statuses as + indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated + to this API version for a complete list of error responses. The applicable + Commonalities Release can be identified in the `API Readiness Checklist` document + associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error + response if it is explicitly documented in the API. + + # Notes for Simple Edge Discovery API publishers + + Should your implementation require the `Port` value to be passed in addition + to the `IP-Address`, please make that explicit in the documentation, and + utilise the `GENERIC_400_MISSING_PORT` error if the `Port` header is omitted. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the provider of the application consuming + the API and the operator's API exposure platform, taking into account the + declared purpose for accessing the API, whilst also being subject to the + prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Further info and support + --- + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA. + url: https://github.com/camaraproject/EdgeCloud + +servers: + - url: "{apiRoot}/simple-edge-discovery/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: | + API root, defined by the service provider, e.g. + `api.example.com` or `api.example.com/somepath` + +tags: + - name: Discovery + description: | + Find the closest Edge Cloud Zone to the user device. + +paths: + /retrieve-closest-edge-cloud-zone: + post: + security: + - openId: + - simple-edge-discovery:read + operationId: readClosestEdgeCloudZone + parameters: + - in: header + name: x-correlator + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + requestBody: + description: Parameters to create a new session + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/RequestBody" + examples: + Identify Device By 3-Legged Access Token: + $ref: '#/components/examples/IdentifyDeviceBy3LeggedToken' + Identify Device By Phone Number: + $ref: '#/components/examples/IdentifyDeviceByPhoneNumber' + Identify Device By IP Address: + $ref: '#/components/examples/IdentifyDeviceByIPAddress' + Identify Device By Multiple Identifiers: + $ref: '#/components/examples/IdentifyDeviceByMultipleIdentifiers' + + responses: + "200": + $ref: "#/components/responses/200Success" + "400": + $ref: "#/components/responses/Generic401" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + + tags: + - Discovery + summary: | + Returns the name of the Edge Cloud Zone closest to user device + identified in the request. + description: | + On receiving this request, the network will return the name + of the Edge Cloud Zone with the shortest network path to the end user + device identified in the request. + +components: + securitySchemes: + openId: + description: Common security scheme for all CAMARA APIs + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + x-correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + EdgeCloudZone: + type: object + description: | + An Edge Cloud Zone, uniquely identified by a combination + of the value of the Edge Resource Name object and the value of the + Provider object (the name of the cloud provider or operator hosting that + edge cloud zone). + properties: + edgeCloudZoneId: + $ref: "#/components/schemas/EdgeCloudZoneId" + edgeCloudZoneName: + $ref: "#/components/schemas/EdgeCloudZoneName" + edgeCloudProvider: + $ref: "#/components/schemas/EdgeCloudProvider" + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + + + EdgeCloudZoneId: + description: | + Operator-issued UUID for the Edge Cloud Zone. + type: string + format: uuid + additionalProperties: false + + EdgeCloudZoneName: + description: | + Edge Cloud Zone Name - the common name for the Edge Cloud Zone. + type: string + additionalProperties: false + + EdgeCloudProvider: + description: | + The company name of the Edge Cloud Zone provider. + type: string + + ErrorInfo: + type: object + description: Error information + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represents + + RequestBody: + description: Common request body to allow optional Device object to be passed + type: object + properties: + device: + $ref: "#/components/schemas/Device" + + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network that the response refers to. This parameter is only returned when the API consumer includes the `device` parameter in their request (i.e. they are using a two-legged access token), and is relevant when more than one device identifier is specified, as only one of those device identifiers is allowed in the response. + + If the API consumer provides more than one device identifier in their request, the API provider must return a single identifier which is the one they are using to fulfil the request, even if the identifiers do not match the same device. API provider does not perform any logic to validate/correlate that the indicated device identifiers match the same device. No error should be returned if the identifiers are otherwise valid to prevent API consumers correlating different identifiers with a given end user. + + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE 1: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + NOTE 2: as for this Commonalities release, we are enforcing that the networkAccessIdentifier is only part of the schema for future-proofing, and CAMARA does not currently allow its use. After the CAMARA meta-release work is concluded and the relevant issues are resolved, its use will need to be explicitly documented in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + PhoneNumber: + description: | + A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + NetworkAccessIdentifier: + description: | + A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + { + "publicAddress": "84.125.93.10", + "publicPort": 59765 + } + + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + + Port: + description: TCP or UDP port number + type: integer + minimum: 1024 + maximum: 65535 + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + DeviceResponseBody: + description: | + The optional device identifier to include in the response + properties: + device: + description: | + The device identifier that was used to fulfil the request. + If this property is not present then the device + identifier sent in the request was used. + allOf: + - $ref: "#/components/schemas/DeviceResponse" + - example: {"phoneNumber": "+123456789"} + + responses: + 200Success: + description: 200 OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + required: + - edgeCloudZoneId + - edgeCloudZoneName + - edgeCloudProvider + allOf: + - $ref: "#/components/schemas/EdgeCloudZone" + - $ref: "#/components/schemas/DeviceResponseBody" + examples: + Closest Edge Cloud details: + description: The details of the closest Edge Cloud Zone + value: + edgeCloudZoneId: "f81d4fae-7dec-11d0-a765-00a0c91e6bf6" + edgeCloudZoneName: "UK-SOUTH" + edgeCloudProvider: "Example Provider" + Closest Edge Cloud plus device identifier: + description: The details of the closest Edge Cloud Zone + and the device identifier used to fulfill the request + value: + edgeCloudZoneId: "f81d4fae-7dec-11d0-a765-00a0c91e6bf6" + edgeCloudZoneName: "UK-SOUTH" + edgeCloudProvider: "Example Provider" + device: + phoneNumber: "+123456789" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + - AUTHENTICATION_REQUIRED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached. + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + IdentifyDeviceBy3LeggedToken: + description: Empty JSON when device is identified by access token + value: + {} + + IdentifyDeviceByPhoneNumber: + description: Identifying device by phone number + value: + device: + phoneNumber: "+123456789" + + IdentifyDeviceByIPAddress: + description: Identifying device by IP address + value: + device: + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + + IdentifyDeviceByMultipleIdentifiers: + description: Identifying device by multiple device identifiers + value: + device: + phoneNumber: "+123456789" + ipv4Address: + publicAddress: "84.125.93.10" + publicPort: 59765 + networkAccessIdentifier: "123456789@domain.com" diff --git a/original/SimpleEdgeDiscovery/documentation/API_documentation/README.MD b/original/SimpleEdgeDiscovery/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SimpleEdgeDiscovery/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md b/original/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..7a6c126b6014bdfae8d54be02b1dff326e54ddc0 --- /dev/null +++ b/original/SimpleEdgeDiscovery/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md @@ -0,0 +1,48 @@ +# Simple Edge Discovery API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to discover (using either my application server/backend service, or an HTTPS application client on the end-user device) the closest Edge Cloud Zone to a given end-user's device. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                            **Actors:** Application service providers, network operators, application developers. The API allows a check to see if end-user consent is required: if consent is required, the end-user will be an actor in the consent flow.
                                                                            + **Scope:** | Get the name of the Edge Cloud Zone closest to a given end-user's device | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                            1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                                            2. The Customer:BusinessManager has successfully subscribed to the Simple Edge Discovery product from the product catalog.
                                                                            3. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                                            4. | +| ***Activities/Steps*** | **Starts when:** The customer application server/client makes a an HTTPS POST request to the Simple Edge Discovery API to query the closest Edge Cloud Zone to the target device (an end-user device). The target device is either identified in the 3-legged access token where supported, or explicitly identified in the encrypted POST request body.
                                                                              **Ends when:** The Simple Edge Discovery API retruns the request information, or an error message. | +| ***Post-conditions*** | Optional - the customer may decide to act upon the information by connecting the end-user application client to the application server instance hosted at the closest Edge Cloud Zone, and/or spin up an application server instance at that closest Edge Cloud Zone if not currently hosted there. | +| ***Exceptions*** | Several exceptions might occur after a request to the Simple Edge Discovery API
                                                                              - Unauthorized: Invalid credentials (e.g. use of already expired access token).
                                                                              - Invalid Input: Invalid input data to retrieve device details (e.g. MSISDN format not as expected, or MSISDN not associated with a customer of the CSP).
                                                                              - Forbidden: End user has not consented to device identifier information being provided to the Customer:User
                                                                              - Service not applicable: the device is not currently attached to an Edge-capable network.
                                                                              - The network cannot resolve the request due to an internal issue.
                                                                              - a rate limit/request quota has been exceeded. | + +## API Workflows +### Simple Edge Discovery +#### Scenario 1: request from application developer server or application client on device + +Constraints: +- Network: cellular (4G/5G) or fixed/Wi-Fi network with an Edge Cloud Zone deployment. +- Application: browser or app calls API over HTTPS +- Northbound Interface only (no 'UNI' client SDK required) + +Note: +- the Edge Cloud Zone platform may be hosted by the operator or a 3rd party hyperscaler (in which case the developer will need an account with that hyperscaler to create instances) + +```mermaid +sequenceDiagram + Note over API Consumer, Operator: PRE device attached
                                                                              to operator network + Note over API Consumer, Operator: PRE App developer registered,
                                                                              authenticated and authorised + alt device identified by 3-legged access token + API Consumer->>Operator: POST /retrieve-closest-edge-cloud-zone + Operator->>Operator: calculate closest Edge Cloud Zone for device + Operator->>API Consumer: edgeCloudZoneID, edgeCloudZoneName, edgeCloudZoneProvider + else device identifier(s) passed in request body + API Consumer->>Operator: POST /retrieve-closest-edge-cloud-zone {request body: device} + Operator->>Operator: calculate closest Edge Cloud Zone for device + Operator->>API Consumer: edgeCloudZoneID, edgeCloudZoneName, edgeCloudZoneProvider, device + end + opt Application developer has a local mapping of server endpoints to Edge Cloud Zone names + Application Developer->>Application Developer: lookup app server endpoint (EdgeCloudZone name) + Application Developer->>Application Client: app server endpoint (IP address:port) + Application Client->>Edge Cloud Zone Provider: connect to app server endpoint (IP address:port) + end + opt spin up instance on closest Edge Cloud Zone + Application Developer->>Edge Cloud Zone Provider: create instance(Edge Cloud Zone) + Edge Cloud Zone Provider->>Application Developer: instance endpoint + Application Developer->>Application Client: instance endpoint + end +``` diff --git a/original/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist.md b/original/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..1dcc7fc21ad10ed0a68111cafa47bf63f4fa6fbf --- /dev/null +++ b/original/SimpleEdgeDiscovery/documentation/API_documentation/simple-edge-discovery_API_Readiness_Checklist.md @@ -0,0 +1,21 @@ +# API Readiness Checklist + +Checklist for simple-edge-discovery v2.0.0 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                              public | stable
                                                                              public | Status | Comments | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/simple-edge-discovery.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | in yaml | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/SimpleEdgeDiscovery_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions) | +| 9 | Test result statement | O | O | O | M | Y | see [issue #128](https://github.com/camaraproject/SimpleEdgeDiscovery/issues/128) | +| 10 | API release numbering convention applied | M | M | M | M | Y | Y | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | Y | see (1) | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/t4HVB) | + +(1) Certified companies can be found at the [GSMA Open Gateway Portal](https://www.open-gateway.com) diff --git a/original/SimpleEdgeDiscovery/documentation/SupportingDocuments/README.MD b/original/SimpleEdgeDiscovery/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SimpleEdgeDiscovery/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SiteToCloudVPN/README.md b/original/SiteToCloudVPN/README.md new file mode 100644 index 0000000000000000000000000000000000000000..a9a28aa744a8b7f561e881a23bb260a4ce1512d3 --- /dev/null +++ b/original/SiteToCloudVPN/README.md @@ -0,0 +1,42 @@ +> [!WARNING] +> **Repository archived** +> +> This repository has been archived following the CAMARA **Lifecycle Clean-up Process** and is kept for reference / maintenance of previous releases only. +> +> - Decision record (API Backlog/TSC): [APIBacklog#284](https://github.com/camaraproject/APIBacklog/issues/284) +> - Lifecycle policy: [Unified Clean-up Process](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#unified-clean-up-process-for-inactive-onboarding-trackers-and-repositories) +> - Reason or Phase of the process: [Phase C – Repository With Partial Progress](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#archival-criteria-per-phase) +> - Request reactivation: submit a new issue in APIBacklog referencing this archived repository: [Reactivation of archived repositories](https://github.com/camaraproject/Governance/blob/main/documentation/API-Onboarding-and-Lifecycle.md#reactivation-of-archived-repositories) + + + + + + + + + + +# SiteToCloudVPN + +Sandbox API Repository to describe, develop, document, and test the SiteToCloudVPN Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/KC3e) + +## Scope +* Service APIs for “Site To Cloud VPN” (see APIBacklog.md) +* It provides the customer with the ability to: + * Instead of ordering a private or customized network service by phone call, or through customer manager manually, this API allows users to create and configure site to cloud network service according to the user request by one click. With the proposed API, when someone calls the API service with network SLA requirements, telecom operators can create non-public cloud leased network service by orchestrating the IP VPN connections of metropolitan network and/or backbone network. + * S2C VPN API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services. Currently most of the use cases are in the field of industries, finance, education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: December 2023 +* Location: virtually + +## Meetings +* Meetings are held virtually +* Schedule: Schedule: Biweekly on Friday, 17:50-18:30(GMT+08:00) CST / 11:50-12:30 CET +* Meeting link: https://teams.live.com/meet/9559310154416?p=X9GldgzTnpV6NUdx / Meeting ID: 955 931 015 441 6 & PWD:V2RXNd + +## Contributorship and mailing list +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/original/SiteToCloudVPN/code/API_definitions/README.MD b/original/SiteToCloudVPN/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..870ff2bb8ece2e8a6c4260c0023dfc5911691cd4 --- /dev/null +++ b/original/SiteToCloudVPN/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definitions and delete this README.MD file diff --git a/original/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_.yaml b/original/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_.yaml new file mode 100644 index 0000000000000000000000000000000000000000..48805d58937ed28a0716c12d2249cd25a2474a7b --- /dev/null +++ b/original/SiteToCloudVPN/code/API_definitions/S2CVPN3_2_.yaml @@ -0,0 +1,936 @@ +openapi: "3.0.3" +info: + title: S2C VPN API + description: | + ##### Before starting to use the API, the developer needs to know about the below specified details : + * S2C VPN service endpoint The URL pointing to the RESTful resource of the S2C VPN API. + * Authentication Security access keys such as OAuth 2.0 client credentials used by client applications to invoke the S2C VPN API. + * Identifier for access point Customer Edge (CE) IPv4 addressand/or IPv6 address of the Customer Edge Router. + * Identifier for the endpoint cloud Provider Edge (PE) IPv4 and/or IPv6 address of the Cloud Provider Edge + * Identifier for the application server(AS)IPv4 and/or IPv6 address of the application server (cloud virtual machine) + * App-Flow (between the application client and application server) The developer wants to have non public network delivery for the precise application data flow for the application users. + * Duration Duration (in hours) for which the S2C VPN session (between CE and cloud PE) should be created. This parameter is optional. When not specified, a default session duration (e.g. 6 months) is applied. The user may request a termination before its expiration. + * Physical Location Physical location of the Customer Edge Router. + + + NOTE- The private physical link between CE and cloud PE is default deployed for one click calling, otherwise it is required to install the physical link, which is out of the scope of this API. + + version: '0.1' +servers: +- url: https://localhost:8080/webapi + description: develop server +paths: + /S2C_VPN_Assessment: + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + isProtected: + type: bool + description: Is S2C VPN protected + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + solution1: + type: array + items: + $ref: '#/components/schemas/S2CVPNAssessment' + example: + - SLA: A + rent: 100 + - SLA: AA + rent: 500 + - SLA: AAA + rent: 800 + solution2: + type: object + properties: + waitdays: + type: integer + description: the waiting-days until the vpn can be offered + minimum: 1 + SLA: + type: string + enum: + - A + - AA + - AAA + rent: + type: integer + description: "VPN monthly rental " + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + /S2C_VPN : + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/S2CVPNOrder' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + resourceGroupId: + type: string + description: resource group Id + cloudGatewayIP: + type: string + description: cloud gateway IPAddress + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + put: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + serviceID: + type: string + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + SLA: + type: string + enum: + - A + - AA + - AAA + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + title: Successful + type: object + properties: + serviceId: + type: string + GuaranteeBandwidth: + type: string + slaLevel: + type: string + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + get: + parameters: + - $ref: '#/components/parameters/X-Correlator' + - $ref: '#/components/parameters/servceId' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + isProtected: + type: bool + description: Is S2C VPN protected + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + purchasedSLA: + type: string + enum: + - A + - AA + - AAA + purchasedGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + purchasedDuration: + type: integer + description: hours + example: 72 + actualSLA: + type: string + enum: + - A + - AA + - AAA + actualGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + actualLatency: + type: integer + description: ms + example: 10 + actualPacketLostRate: + type: number + description: '%' + example: 0.1% + servicedDuration: + type: integer + description: hours + example: 24 + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' + delete: + parameters: + - $ref: '#/components/parameters/X-Correlator' + - $ref: '#/components/parameters/servceId' + responses: + '200': + description: Successful response + headers: + X-Correlator: + description: When the API Consumer includes the "X-Correlator" header in the request, the API provider must include it in the response with the same value that was used in the request + schema: + type: integer + content: + application/json: + schema: + type: object + properties: + serviceId: + type: string + description: service Id + isProtected: + type: bool + description: Is S2C VPN protected + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + actualSLA: + type: string + enum: + - A + - AA + - AAA + actualGuaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + actualLatency: + type: integer + description: ms + example: 10 + actualPacketLostRate: + type: number + description: '%' + example: 0.1% + servicedDuration: + type: integer + description: hours + example: 24 + '400': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/InvalidArgument' + '401': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/AuthenticationRequired' + '403': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/PermissionDenied' + '404': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/NotFound' + '500': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Internal' + '503': + description: error/exception codes for the S2C VPN AP + content: + application/json: + schema: + $ref: '#/components/responses/Unavailable' +components: + parameters: + X-Correlator: + name: X-Correlator + required: true + in: header + description: "Service correlator to make E2E observability,Recommendation is to use UUID for values,for example:b4333c46-49c0-4f62-80d7-f0ef930f1c46" + schema: + type: string + servceId: + name: servceId + required: true + in: query + description: "service session ID" + schema: + type: string + servceName: + name: servceName + required: true + in: query + description: "servce name" + schema: + type: string + isProtected: + name: isProtected + required: true + in: query + description: Is S2C VPN protected + schema: + type: bool + CEType: + name: CEType + required: true + in: query + description: S2C VPN access point type + schema: + type: string + enum: + - site + - cloud + primaryCEIP: + name: primaryCEIP + required: true + in: query + description: primary Access point CE address + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + secondaryCEIP: + name: secondaryCEIP + required: false + in: query + description: secondary Access point CE address. When isProtected is true, secondaryCEIP is required + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + PEType: + name: PEType + required: true + in: query + description: S2C VPN endpoint type ( Cloud PE/gateway type) + schema: + type: string + enum: + - site + - cloud + primaryPEIP: + name: primaryPEIP + required: true + in: query + description: primary Endpoint Cloud PE address + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + secondaryPEIP: + name: secondaryPEIP + required: false + in: query + description: secondary Endpoint Cloud PE address. When isProtected is true, secondaryPEIP is required + schema: + $ref: '#/components/schemas/SingleIpv4Addr' + sla: + name: slaLevel + required: true + in: query + description: "available SLA (Service-Level Agreement)" + schema: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + name: GuaranteeBandwidth + required: true + in: query + description: Guarantee Bandwidth (Mps) + schema: + type: integer + minimum: 1 + duration: + name: duration + required: true + in: query + description: "Guarantee duration, unit:Hour" + schema: + type: integer + CELocation: + name: CELocation + required: true + in: query + description: Access point CE physical location + schema: + type: string + routeProtocal: + name: routeProtocal + required: true + in: query + description: routeProtocal + schema: + type: string + enum: + - static + - BGP + + schemas: + TimePeriod: + properties: + startDate: + type: string + format: date-time + description: An instant of time, starting of the TimePeriod. + endDate: + type: string + format: date-time + description: An instant of time, ending of the TimePeriod. If not included, then the period has no ending date. + required: + - startDate + ErrorInfo: + type: object + properties: + message: + type: string + description: A human readable description of what the event represent + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + required: + - message + - status + - code + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any single IPv6 address from within the subnet allocated to the device (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP address and port as seen by the application server, or the private (local) and any public (observed) IP addresses in use by the device (this information can be obtained by various means, for example from some DNS servers). + + If the allocated and observed IP addresses are the same (i.e. NAT is not in use) then the same address should be specified for both publicAddress and privateAddress. + + If NAT64 is in use, the device should be identified by its publicAddress and publicPort, or separately by its allocated IPv6 address (field ipv6Address of the Device object) + + In all cases, publicAddress must be specified, along with at least one of either privateAddress or publicPort, dependent upon which is known. In general, mobile devices cannot be identified by their public IPv4 address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile network. In 3GPP terminology, it corresponds to the GPSI formatted with the External Identifier ({Local Identifier}@{Domain Identifier}). Unlike the telephone number, the network access identifier is not subjected to portability ruling in force, and is individually managed by each operator. + type: string + example: "123456789@domain.com" + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE: the MNO might support only a subset of these options. The API invoker can provide multiple identifiers to be compatible across different MNOs. In this case the identifiers MUST belong to the same device. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + + S2CVPNAssessment: + type: object + properties: + SLA: + type: string + enum: + - A + - AA + - AAA + rent: + type: integer + description: "VPN monthly rental " + S2CVPNOrder: + type: object + properties: + servceName: + type: string + description: "servce name" + isProtected: + type: bool + description: Is S2C VPN protected + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + primaryCEIP: + description: primary Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryCEIP: + description: secondary Access point CE address + type: string + format: ipv4 + example: "84.125.94.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + primaryPEIP: + description: primary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + secondaryPEIP: + description: secondary Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.94.10" + SLA: + type: string + enum: + - A + - AA + - AAA + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + routeProtocal: + type: string + enum: + - static + - BGP + + responses: + InvalidArgument: + description: Invalid Argument + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 400 + code: INVALID_INPUT + message: | + - Expected property is missing: Site or cloud 's ipv4addr/ipv6addr + Conflict: + description: conflict + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 409 + code: CONFLICT + message: Schema validation failed at ... + AuthenticationRequired: + description: Authentication Required + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required + PermissionDenied: + description: Permission denied + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + NotFound: + description: Not Found + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + MethodNotAllowed: + description: Method not allowed + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target + NotAcceptable: + description: Not Acceptable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 406 + code: NOT_ACCEPTABLE + message: The server can't produce a response matching the content requested by the client through Accept-* headers + UnsupportedMediaType: + description: Unsupported Media Type + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Internal: + description: Internal Error + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 500 + code: INTERNAL + message: Unknown server error.Typically a server bug. + BadGateway: + description: Bad Gateway + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 502 + code: BAD_GATEWAY + message: Couldn't reach an upstream internal service. + Unavailable: + description: Service Unavailable + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 503 + code: UNAVAILABLE + message: Service unavailable + Timeout: + description: Timeout + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + example: + status: 504 + code: TIMEOUT + message: Request timeout exceeded + + + + + + + + \ No newline at end of file diff --git a/original/SiteToCloudVPN/documentation/API_documentation/README.MD b/original/SiteToCloudVPN/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story.md b/original/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..fd54c53495a796884b9b6494b25b8f36c723e5b2 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/API_documentation/S2CVPN_User_Story.md @@ -0,0 +1,10 @@ +# SiteToCloud(S2C) VPN API User Story + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer or industry customer, I want to request (using my application server/backend service)cloud leased network connection service between siteA/cloudA and siteB/cloudB from a Communication Service Provider (CSP), so that I can ensure better and more reliable quality for our end users at any required time with proper cost. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                              **Actors:** Application service providers, industry customer, application developers.
                                                                              **Scope:** Site to Cloud VPN Service Booking(check network availability level, resource availability and corresponding fees ) \- Create/Remove/Modify/Query service instance (S2C VPN session resource) | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                              1. The Customer:BusinessManager and Customer:Administrator have been onboarded to the CSP's API platform.
                                                                              2. The Customer:Administrator has onboarded the Customer:User to the platform.
                                                                              3. The Customer either owns the device subscriptions or has agreed to the terms and conditions of the CSP for managing consent of subscription owners.
                                                                              4. The means to get the access token are known to the Customer:User to ensure secure access of the API.| +| ***Activities/Steps*** | **Starts when:** The customer application server makes a POST request (including required service area(access node and end node ), bandwidth requirements,etc) to the S2C VPN service provision creation API to create a new S2C VPN session resource.
                                                                                **Ends when:**  The customer application server makes a DELETE request to the S2C VPN service deletion API , or the S2C VPN service deletion session resource deletion was triggered automatically either because the customer specified duration has expired or the default expiration limit set by the S2C VPN service provider has reached. | +| ***Post-conditions*** | The specified App-Flow was provided stable and private network( required bandwidth and latency) connection to computing/storage services on the cloud and if callback URL was specified, a S2C VPN session resource termination notification was received at the end. | +| ***Exceptions*** | Several exceptions might occur during the S2C VPN API operations
                                                                                - Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                                - Invalid input: Not valid input data to invoke operation (e.g. IP address format not as expected).
                                                                                - Session-not-created: Due to other internal errors or insufficient resources , S2C VPN session resource could not be created | diff --git a/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12.md b/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12.md new file mode 100644 index 0000000000000000000000000000000000000000..5a7143ed7f71dc5413b6c1b7f89d9e70d5700dc1 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-04-12.md @@ -0,0 +1,29 @@ +# Site To Cloud VPN Meeting - MOM-2024-04-12 + +*Friday, April 12th, 2024* + +## Attendees (probably incomplete) + +* Dan Xu (China Telecom) +* Fan Yang (China Unicom) +* Shuting Qing (Huawei) +* Jin Xu (Huawei) +* ... + +## Agenda +* Review API documentation of S2C VPN API pr#11, issues [#8](https://github.com/camaraproject/SiteToCloudVPN/issues/8) +* Review initial Yaml of Site to Cloud VPN API #10, issues [#9](https://github.com/camaraproject/SiteToCloudVPN/issues/9) +* AOB + + + +## Discussion + +1. The scope of the Site To Cloud VPN, for example, for API creation, should the endpoint of Site To Cloud VPN be the cloud provider edge(PE) or the cloud virtual machine? + + Huawei experts pointed that cloud PE is in the management scope of network controllers, while cloud virtual machine is the management scope of cloud management system, so cloud PE as the endpoint will be a easier way to complete the API. + +## AOB +1. The next call will be on Friday, April 26th, 15:30-16:30(GMT+08:00) CST / 9:30-10:30 CET + + \ No newline at end of file diff --git a/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524.md b/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524.md new file mode 100644 index 0000000000000000000000000000000000000000..7aebee626f014abbdf52a55e80d3966fc653cb24 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/MeetingMinutes/MOM-2024-0524.md @@ -0,0 +1,80 @@ +# Site To Cloud VPN Meeting - MOM-2024-04-12 + +*Friday, May 24th, 2024* + +## Attendees (probably incomplete) + +* Dan Xu (China Telecom) + +* Shuting Qing (Huawei) + +* Jin Xu (Huawei) + + + +## Agenda +* Discuss the input and output parameters pr#13 +* Dissuss issues [#17](https://github.com/camaraproject/SiteToCloudVPN/issues/17) +* AOB + + + +## Discussion + +* Regarding the description and definition of S2C VPN access point and S2C VPN endpoint, both of them can be site or cloud, therefore, this API natively support the cloud to cloud connection scenarios. + +* Need to further consider whether more input parameters are needed + +​ + +## Appendix + +Request Body of S2C_VPN_Assessment + +- url: https://localhost:8080/webapi + description: develop server + paths: + /S2C_VPN_Assessment: + post: + parameters: + - $ref: '#/components/parameters/X-Correlator' + requestBody: + content: + application/json: + schema: + type: object + properties: + CEType: + type: string + description: S2C VPN access point type + enum: + - site + - cloud + CEIP: + description: Access point CE address + type: string + format: ipv4 + example: "84.125.93.10" + PEType: + type: string + description: S2C VPN endpoint type ( Cloud PE/gateway type) + enum: + - site + - cloud + PEIP:: + description: Endpoint Cloud PE address + type: string + format: ipv4 + example: "84.125.93.10" + guaranteeBandwidth: + type: integer + description: Guarantee Bandwidth (Mps) + minimum: 1 + duration: + type: integer + description: "Guarantee duration, unit:Hour" + CELocation: + type: string + + + diff --git a/original/SiteToCloudVPN/documentation/MeetingMinutes/README.MD b/original/SiteToCloudVPN/documentation/MeetingMinutes/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/MeetingMinutes/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN.md b/original/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN.md new file mode 100644 index 0000000000000000000000000000000000000000..d5364518818c5b92d96c32d2b357f346679cfd97 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/SupportingDocuments/APIproposal_Site_to_cloud_S2C_VPN.md @@ -0,0 +1,11 @@ +| **Field** | Description | +| :---------------------------------------- | ------------------------------------------------------------ | +| API family name | Site to cloud (S2C) VPN | +| API family owner | China Telecom, Huawei | +| API family summary | **High level description**
                                                                                Instead of ordering a private or customized network service by phone call, or through customer manager manually, this API allows users to create and configure site to cloud network service according to the user request by one click. With the proposed API, when someone calls the API service with network SLA requirements, telecom operators can create non-public cloud leased network service by orchestrating the IP VPN connections of metropolitan network and/or backbone network.
                                                                                S2C VPN API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services. Currently most of the use cases are in the field of industries, finance, education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc.

                                                                                **Input params**
                                                                                service name, access node type, access node ip address, end node type, end node ip address, network availability level, bandwidth, duration, routing protocol, access node GIS address/ID.

                                                                                **Output params**
                                                                                API call success or failure response, service Id, resource Id

                                                                                | +| Technical viability | This API uses existing IP VPN connection creation capabilities of MAN(Metropolitan Area Network) and backbone network in operators. | +| Commercial viability | This API is suitable to multi-sites, industries and applications which require private network service ( large bandwidth, low latency, high guarantee and security), fast and flexible on-demand service provisioning. The original customers can choose traditional product delivery mode or Service on Demand API mode. The new customers will use Service on Demand API mode which is easy to use. | +| YAML code available? | TBD | +| Validated in lab/productive environments? | YES, validated in lab environment | +| Validated with real customers? | No | +| Validated with operators? | No with other operators. | \ No newline at end of file diff --git a/original/SiteToCloudVPN/documentation/SupportingDocuments/README.MD b/original/SiteToCloudVPN/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SiteToCloudVPN/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements.md b/original/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements.md new file mode 100644 index 0000000000000000000000000000000000000000..1710632199b7d136f4ca9cc98b50d6fb45da696d --- /dev/null +++ b/original/SiteToCloudVPN/documentation/SupportingDocuments/S2C_VPN-use_cases_and_requirements.md @@ -0,0 +1,18 @@ +# Site To Cloud (S2C) VPN + +This API aims to provide multi-site, multi-cloud network connection for customers, and provide virtual private network services for industries and applications such as education, medical, Internet of things, cloud desktop, cloud conference, cloud recording and etc. + +## Use cases and requirements + +#### Data storage scenarios + +- Overview + + There are two typical application scenarios: + + 1. For backup and storage scenarios of cold data that has not been used for a long time, the data needs to be backed up and stored on a cloud with reliable network connectivity. + 1. When the distributed cloud resources usage rate is unbalanced, local video streams are scheduled to cloud nodes with sufficient resources for storage + +- Requirements: + + - For data storage applications(such as video, voice, and images storage), it is needed to create the stable data transmission network to access cloud resources that meet the storage and network requirements of the application/capability invokers by S2C VPN API. For example, for cloud court application that demands to deliver trial video materials to the central cloud, the network delay is required to lower than 50ms and bandwidth is higher than 20Mbps , so cloud court application is suitable to call S2C VPN API to achieve elastic, private and secure data delivery and storage. \ No newline at end of file diff --git a/original/SponsoredData/README.md b/original/SponsoredData/README.md new file mode 100644 index 0000000000000000000000000000000000000000..47a67a63d89a360a70cfe6e732f06a337e38ffa7 --- /dev/null +++ b/original/SponsoredData/README.md @@ -0,0 +1,62 @@ + + + + + + + + + +# SponsoredData + +Sandbox API Repository to describe, develop, document, and test the **Sponsored Data Service API(s)**. This repository currently belongs to the *Sandbox* stage and is under active development within the CAMARA framework. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/f4CVDg) + +## Scope + +The **Sponsored Data** API enables a sponsoring company to cover the data usage of end users for a defined period and/or data volume, thereby strengthening its brand presence and enhancing the user experience. + +The API is organized into three hierarchical levels: + +- **Sponsor:** The company that finances the sponsored data usage. +- **Campaigns:** Sets of sponsorship actions contracted by sponsors for various commercial or marketing purposes. +- **Sponsored Subscribers:** Individual users participating in a campaign, who opt in to receive sponsored data for a defined volume and duration. The sponsorship is always activated upon the user’s explicit choice or consent. + +Campaigns can follow one of two commercial models: + +Campaigns can be organized under different commercial models, depending on the sponsorship agreement between the Sponsor and the Operator: + +- **Prepaid** — The Sponsor pre-purchases a total data volume, from which units are deducted as sponsored sessions are started and consumed. +- **Postpaid** — The Sponsor is billed at the end of the campaign cycle based on the actual sponsored data consumption. + +The API supports the following operations: + +- `/start-sponsorship` +- `/session-status` +- `/revoke-sponsorship` +- `/campaign-status` +- `/active-sponsorships` +- `/configure-alerts` +- `/campaign-management` + +Identifiers such as **Sponsor_Id**, **Campaign_ID** and **Session_ID** are generated and managed by the Operator Platform (MNO). + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: Bi-Weekly on Fridays at 14:00 UTC + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://github.com/camaraproject/SponsoredData/tree/main/documentation/MeetingMinutes) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/SponsoredData/code/API_definitions/README.MD b/original/SponsoredData/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/SponsoredData/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/SponsoredData/code/API_definitions/sponsored_data.yaml b/original/SponsoredData/code/API_definitions/sponsored_data.yaml new file mode 100644 index 0000000000000000000000000000000000000000..0b92fceec5c7525a101de2d9ceb02c69c189a3d4 --- /dev/null +++ b/original/SponsoredData/code/API_definitions/sponsored_data.yaml @@ -0,0 +1,1338 @@ +openapi: 3.0.3 +info: + title: Sponsored Data API + version: wip + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + + description: | + + Sponsored Data API for OpenGateway/CAMARA Project + + The Sponsored Data API allows sponsoring companies (EPs) to cover the cost of mobile data access for end-users on 4G and 5G networks. This API is part of the Open Gateway/CAMARA initiative and provides a set of operations for the dynamic management of mobile data sponsorship. Sponsoring companies can start or revoke sponsorships for users, as well as query the status of both sponsorship sessions and their campaigns. + + The API also allows for the verification of user eligibility for sponsorship and the ability to pause and resume active campaigns. With this API, mobile operators can offer differentiated services that enable innovative business models, providing connectivity at no direct cost to the end-user, with funding provided by a sponsoring entity. + + This service is ideal for advertising campaigns, product promotions, or services. + + Objective of This Initial Version + In this initial version of the API, the sponsorship is proposed for all data traffic (ANY) carried by the user's default bearer, for a specified volume and time, without focusing on a specific destination. + + * Onboarding * + Onboarding is the process by which a Sponsoring Company (EP) contracts a Sponsorship Campaign with the API Gateway Platform (OpenGateway) and the specific Mobile Network Operator (MNO). Initially, this event is supported by the signing of an agreement or documentation outlining the general objectives of the campaign and default sponsorship conditions. For example: + + Type of Campaign: Prepaid or postpaid + Total data volume contracted for prepaid campaigns, e.g., 2000 MB + Campaign validity, e.g., (from/to) or (336 total hours consumed since activation) + Default sponsored data volume for users, e.g., 50 MB + Default sponsorship validity per user, e.g., 10 minutes + Additionally, during this onboarding process, the EP is provided with the "sponsorId" and the specific "campaign_Id". + + * campaignId * + Campaign_ID is a unique identifier assigned to each sponsorship campaign contracted by a Sponsoring Company and assigned during the onboarding process. + + * Traceability - sessionId * + All operations associated with a user (UE) sponsorship are grouped under a session identified by a sessionId. This identifier allows tracking and correlating all interactions within the same sponsorship session. + + * Assignment of Identifiers * + Both, campaign_Id and sessionId, are assigned and managed exclusively by the API Gateway Platforms (OpenGateway) and communicated to both the Sponsoring Companies and the MNOs. CampaignId during the onboarding document signing proccess. And sessionId on real time during each sponsorship operation request. + + * Authorization and Authentication * + The "Camara Security and Interoperability Profile" provides details on how a client requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the Profile. + + The specific authorization flows to be used will be determined during the onboarding process, occurring between the API Client and the Telco Operator exposing the API, taking into account the declared purpose for accessing the API, and subject to the prevailing legal framework dictated by local legislation. + + It is important to note that in cases where personal user data is processed by the API, and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of 3-legged access tokens becomes mandatory. This measure ensures that the API remains in strict compliance with user privacy preferences and regulatory obligations, upholding the principles of transparency and user-centric data control. + + * Authorization and Consent Approach * + The Sponsored Data API facilitates user-initiated sponsorship of data services, requiring active user engagement at specific moments via the sponsor’s application. Given the nature of this service, where users must explicitly request sponsorship, the "Authorization Code Flow - Frontend Flow" has been chosen as the authorization and consent method. This flow aligns with the need for secure, direct interaction between the user and the service, ensuring that consent is explicitly provided in a manner that complies with data protection regulations such as GDPR. + + * API Functionality * + This API exposes the following endpoints: NOTE: All of these are REQUIRED for minimal and correct operation unless explicitly indicated otherwise [OPTIONAL OPERATION] + + /sponsorship: Initiates sponsorship and includes a webhook for session-related notifications. With HTTP 201, the Gateway Platform returns the sessionId. + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/session-status: Queries the status of a particular session. Returns session-related data. + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/revoke: Revokes an active sponsorship session. If active, it must be terminated. + /campaign/{sponsorId}/{campaignId}/status: Queries the status of the campaign, returning whether it is active, paused, or completed. Includes data such as campaign start and end time, consumed data volume, and additional information. The contracted data volume and remaining data volume are included only for prepaid campaigns. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/active-sponsorship-list: Queries the list of users currently sponsored by the campaign. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/alert-subscription: Requests subscription to events associated with the campaign. Includes a webhook for notifications. In this version of the API, only consumption thresholds and expiration events are available. [OPTIONAL OPERATION] + /campaign/{sponsorId}/{campaignId}/manage: Allows pausing and reactivating a campaign. During onboarding, it should be defined whether paused periods consume campaign validity time. [OPTIONAL OPERATION] + + * Date and Time Formats * + All date and time values in this API are represented using the ISO 8601 format. For example, '2023-11-22T13:37:00Z' represents November 22, 2023 at 1:37 PM UTC. + + * Roles * + Mobile Network Operators (MNOs): Providers of mobile services that manage network infrastructure and data provisioning. + Sponsoring Companies (SCs): Companies that fund the use of mobile data for their clients or specific users, aiming to offer a no-cost data experience. + API Gateway Operator Platform (OpenGateway level): A gateway with various functions based on best business practices established by OpenGateway. In addition to translation functions, it must track and manage campaigns and sessions established during operation. + Sponsored Users (SU): Mobile network users whose mobile data usage is sponsored by the EPs. + +servers: + - url: "{apiRoot}/sponsored-data/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root, defined by the service provider, e.g. `api.example.com` or `api.example.com/somepath` + +tags: + - name: Sponsorship Management + description: Operations related to starting, revoking, and monitoring sponsorship sessions. + - name: Campaign Management + description: Operations for managing sponsorship campaigns and alerts. + - name: Reporting + description: Operations for querying balances, usage, and active sessions. + +paths: + + /sponsorship: + post: + tags: + - Sponsorship Management + summary: Start Sponsorship Session Request + description: This operation requests the sponsorship for a subscriber in a specific campaign, allowing them to use sponsored data within the limits set by this request or those defined in the campaign onboarding declaration by default. + operationId: startSponsorship + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + requestBody: + description: Parameters for creating the new sponsorship session + required: true + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + dataVolume: + description: Data volume (in MegaBytes) to be sponsored by the sponsor for the mobile user. If not specified, the default data volume defined in the onboarding rules will apply. + type: integer + minimum: 1 + maximum: 1000 + duration: + description: Duration (in minutes) of the requested sponsorship. If not specified, the duration defined in the onboarding rules will apply. + type: integer + minimum: 1 + maximum: 1440 + webhookUrl: + $ref: '#/components/schemas/WebhookUrl' + callbackToken: + description: Security token for authenticating notifications sent to the webhook. + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" # UUID versión 4 regular expression + required: + - sponsorId + - campaignId + - phoneNumber + - webhookUrl + - callbackToken + callbacks: + notifications: + "{$request.body#/webhookUrl}": + post: + tags: + - Sponsorship notifications callback + summary: "Sponsorship notifications callback" + description: | + This endpoint must be implemented by the API consumer. The sponsorship server will send notifications to this URI when a sponsorship ends, providing the reason for termination and session details + operationId: notifySponsorshipEnd + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: "#/components/parameters/x-callbackToken" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SponsorshipEndNotification" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + responses: + '201': + description: Successful operation. New sponsorship session created. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + + sponsoredDataVolume: + description: The assigned data volume for the user. This value is derived from either the sponsorship request or, if not specified in the request, from the default value defined in the campaign profile during onboarding. + type: integer + minimum: 1 + maximum: 1000 + required: + - sponsorId + - campaignId + - sessionId + - startTime + - endTime + - sponsoredDataVolume + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/session-status: + get: + tags: + - Reporting + summary: Sponsorship Session Status Inquiry + description: | + Queries detailed information about a sponsorship session for a specific campaign and sponsor. + NOTES: + The access token for this query must be a 2-legged token, and the sponsor must have been previously authorized with a 3-legged token at the time of session initiation. + The session must have been created by the same API client indicated in the access token. + operationId: getSessionStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + - name: sessionId + description: Unique identifier of the sponsorship session. + in: path + required: true + schema: + $ref: '#/components/schemas/SessionId' + responses: + "200": + description: Contains information about the sponsorship session + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + sessionStatus: + description: Indicates whether the session is active or inactive. + enum: + - active + - inactive + dataVolumeConsumed: + description: Volume of data consumed in the session. (MBytes) + type: integer + dataVolumeAvailable: + description: Volume of remaining available data in the session. (MBytes) + type: integer + endReason: + description: Reason for session termination, if it is no longer active. + enum: + - validity_expired + - data_exhausted + - session_revoked + - not_available + required: + - phoneNumber + - startTime + - endTime + - sessionStatus + - dataVolumeConsumed + - dataVolumeAvailable + examples: + session_active: + description: Session still active + value: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541149924576" + startTime: "2024-09-01T12:00:00Z" + endTime: "2024-09-01T14:00:00Z" + sessionStatus: "active" + dataVolumeConsumed: 60 + dataVolumeAvailable: 40 + endReason: not_available + session_inactive: + description: Session still active + value: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541149924576" + startTime: "2024-09-01T12:00:00Z" + endTime: "2024-09-01T13:03:00Z" + sessionStatus: "inactive" + dataVolumeConsumed: 100 + dataVolumeAvailable: 0 + endReason: data_exhausted + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /sponsorship/{sponsorId}/{campaignId}/{sessionId}/revoke: + delete: + tags: + - Sponsorship Management + summary: Revocation of Sponsorship + description: This operation revokes an active sponsorship, preventing further use of sponsored data for the subscriber. + operationId: revokeSponsorship + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + - name: sessionId + description: Unique identifier of the sponsorship session. + in: path + required: true + schema: + $ref: '#/components/schemas/SessionId' + responses: + '200': + description: Session revoked successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + + requestResult: + type: string + enum: + - successful_revocation + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/campaign-status: + get: + tags: + - Reporting + summary: Campaign Status Inquiry [active, paused, concluded], data volume balance. + description: > + Retrieves the current status of a specific sponsorship campaign for a given sponsor. + Provides information such as whether the campaign is active, paused, or completed, along with key metadata like start and end dates, data volume limits, and any configured alerts. This endpoint allows sponsoring companies to monitor the progress and operational state of their campaigns. + operationId: getCampaignStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + responses: + '200': + description: Returns the status of the campaign + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + status: + type: string + description: Current status of the campaign (e.g., "active", "paused", "completed"). + enum: + - active # The campaign is currently ongoing. + - paused # The campaign is temporarily halted. Active sponsorships continue until completion, and the campaign's duration does not extend due to this pause. + - completed # The campaign has finished successfully, either because all contracted data has been consumed or the time limit has been reached. This status could be sufficient to indicate that the campaign has ended. + - not_available + startTime: + $ref: "#/components/schemas/Time" + endTime: + $ref: "#/components/schemas/Time" + campaignType: + description: Indicates whether the campaign is prepaid or postpaid + type: string + enum: + - prepaid + - postpaid + contractedDataVolume: + type: integer + description: Total data volume contracted for the campaign in MegaBytes. This field is REQUIRED only for prepaid campaigns. + usedDataVolume: + type: integer + description: Total data volume consumed in the campaign, in megabytes (MB), as allocated for sponsorships. + remainingDataVolume: + type: integer + description: Remaining data volume available for the campaign in MegaBytes. This field is REQUIRED only for prepaid campaigns. + completionReason: + type: string + description: Reason for completion (e.g., "time expired", "data exhausted"). + enum: + - time_expired + - data_exhausted + - not_available # if the campaign is still active or paused + required: + - sponsorId + - campaignId + - status + - startTime + - endTime + - usedDataVolume + - completionReason + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/active-sponsorships: + get: + tags: + - Reporting + summary: Query of Active Sponsorships + description: > + Returns the list of users currently benefiting from sponsored data under a specific campaign. Each entry includes identifiers and session information to track which end users are actively consuming sponsored data. Useful for reporting and campaign analytics. + operationId: getActiveSponsorships + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + responses: + '200': + description: List of users currently sponsored by the campaign. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + activeSponsorships: + type: array + items: + type: object + properties: + sessionId: + $ref: '#/components/schemas/SessionId' + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + totalCount: + description: Total number of sponsored subscribers currently. + type: integer + example: 5000 + example: + sponsorId: "3fa85f64-5717-4562-b3fc-2c963f66afaf@company.com" + campaignId: "3fa85f64-5717-4562-b3fc-2c963f663faf@company.com" + activeSponsorships: + - sessionId: "123e4567-e89b-12d3-a456-426614174000" + phoneNumber: "+541100000001" + - sessionId: "123e4567-e89b-12d3-a456-426614174003" + phoneNumber: "+541100000002" + - sessionId: "123e4567-e89b-12d3-a456-426614174008" + phoneNumber: "+541100000003" + totalCount: 3 + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/{sponsorId}/{campaignId}/alert-subscription: + post: + tags: + - Campaign Management + summary: Campaigns - Subscription to Alert y Notifications + description: | + This operation enables Sponsors (EPs) to subscribe to receive notifications related to campaigns. With the subscription, the EP provides a webhook URL and a token, which will be used by the API Gateway to send notifications related to the campaign. + In this API version, only two types of alerts are provided: + - Notification for consuming more than 80% of the contracted data volume. + - Notification for campaign validity expiration. + - Notification for campaign data volume exhausted. + - Alerts for network failures will be addressed in future versions. + operationId: configureAlerts + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + - name: sponsorId + in: path + required: true + description: Unique identifier of the sponsor company. + schema: + $ref: '#/components/schemas/SponsorId' + - name: campaignId + description: Unique identifier of the sponsorship campaign. + in: path + required: true + schema: + $ref: '#/components/schemas/CampaignId' + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + webhookUrl: + $ref: '#/components/schemas/WebhookUrl' + callbackToken: + type: string + description: Security token to authenticate notifications sent to the webhook. + alertDataVolumeThresholds: + type: boolean + description: Indicates whether a notification should be sent when data consumption exceeds 80% of the contracted amount (applicable for prepaid campaigns).. + example: true + campaignExpiryNotification: + type: boolean + description: Indicates whether a notification should be sent when the campaign expires. + example: true + dataVolumeExhausted: + type: boolean + description: Indicates whether a notification should be sent when the campaign data volume is exhausted. + example: true + callbacks: + notifications: + "{$request.body#/webhookUrl}": + post: + tags: + - Campaign notifications callback + summary: "Callback definition for campaign notifications (webhookUrl)" + description: > + This endpoint must be implemented by the API consumer. The server will send notifications to this URL with the token provided in the subscription to authenticate the request. + operationId: notifyCampaignEvent + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-callbackToken' + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/CampaignNotification" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + notifications: + enum: + - alertDataVolumeThresholds + - campaignExpiryNotification + - dataVolumeExhausted + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "500": + $ref: "#/components/responses/Generic500" + "503": + $ref: "#/components/responses/Generic503" + responses: + '200': + description: Campaign notifications subscription - SUCCESS + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + requestResult: + type: string + example: "Campaign notifications subscription - SUCCESS" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + + /campaign/management: + post: + tags: + - Campaign Management + summary: Campaign Management + description: > + This operation allows pausing or resuming a campaign based on the action parameter provided in the request body. The possible values for action are: + - PAUSE to temporarily halt new sponsorships (ongoing sponsorships will continue until completion). + - RESUME to reactivate the campaign. + If the campaign has already ended, the API will respond with a 400 error, indicating that the campaign is finished and cannot be modified. Pausing a campaign does not extend its end date or overall duration. + operationId: manageCampaign + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/x-accessToken' + requestBody: + description: Parameters to manage the campaign. + required: true + content: + application/json: + schema: + type: object + properties: + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + action: + type: string + enum: + - pause + - resume + description: "The action to be performed on the campaign. It can be 'PAUSE' to pause or 'RESUME' to resume." + responses: + '200': + description: Successful operation + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: object + properties: + requestResult: + type: string + example: "CAMPAIGN PAUSED SUCCESSFULLY or CAMPAIGN RESUMED SUCCESSFULLY" + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + startTime: + $ref: "#/components/schemas/Time" + status: + type: string + description: Current status of the campaign (e.g., "active", "paused", "completed"). + enum: + - paused + - resumed + - completed + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "405": + $ref: "#/components/responses/Generic405" + "406": + $ref: "#/components/responses/Generic406" + "415": + $ref: "#/components/responses/Generic415" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + "500": + $ref: "#/components/responses/Generic500" + "501": + $ref: "#/components/responses/Generic501" + "502": + $ref: "#/components/responses/Generic502" + "503": + $ref: "#/components/responses/Generic503" + "504": + $ref: "#/components/responses/Generic504" + +components: + + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation identifier in UUID version 4 format + required: true + schema: + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" # UUID versión 4 regular expression + x-accessToken: + name: accessToken + in: header + description: Access token for the Sponsor. + required: true + schema: + type: string + x-callbackToken: + name: x-callbackToken + in: header + description: | + Security token for authenticating the notification. It must match the value provided in the callbackToken field of the initial sponsorship request body. + required: true + schema: + type: string + format: uri + example: https://tonys-server.com + headers: + x-correlator: + description: | + A unique identifier used to correlate requests and responses across the API. + Useful for tracing, debugging, and ensuring consistency between sponsor operations and system events. + required: true + schema: + type: string + format: "uuid" + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-4[0-9a-fA-F]{3}-[89aAbB][0-9a-fA-F]{3}-[0-9a-fA-F]{12}$" + schemas: + SponsorId: + type: string + description: Unique sponsor identifier, assigned by the API GW Platform operator. Should include a domain associated with the company for easy recognition. + pattern: "^[a-zA-Z0-9._%+-]+@[a-zA-Z0-9.-]+\\.[a-zA-Z]{2,}$" # Excample 'ID@sponsor_domain.com' + CampaignId: + type: string + description: Unique identifier for the campaign, including a UUID and the sponsor's domain. + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12}@[a-zA-Z0-9.-]+\\.[a-zA-Z]{2,}$" # Example "UUID@sponsor_domain.com" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + SessionId: + description: Unique session identifier, assigned by the API GW Platform operator. Should include a domain associated with the company for easy recognition. + type: string + format: uuid + pattern: "^[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12}$" + CampaignNotification: + description: | + Provides details about a campaign-related event or alert, such as nearing data limits, expiration of the campaign, or other operational notifications. Intended to keep sponsors informed about relevant changes or milestones in their campaigns. + type: object + properties: + api_version: + description: Data Sponsored API Version (must be 1.0.0) + type: string + enum: + - '1.0.0' + datacontenttype: + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + type: string + enum: + - 'application/json' + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + type: string + description: Identificador de la campaña. + eventType: + type: string + description: Tipo de evento que desencadenó la notificación. + enum: + - DATA_VOLUME_THRESHOLD_EXCEEDED (80%) + - DATA_VOLUME_EXHASTED + - CAMPAIGN_EXPIRED + timestamp: + type: string + format: date-time + description: Fecha y hora en que ocurrió el evento. + ErrorInfo: + description: The error object used for error-cases. + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + WebhookUrl: + type: string + format: url + description: The URL to which notifications about session status changes will be sent using the HTTP protocol. (e.g., session termination) + example: "https://sponsor.endpoint.example.com/webhook" + SponsorshipEndNotification: + description: > + Contains information about the conclusion of a sponsored data session for a user. + Includes the reason for ending the sponsorship, session identifiers, and relevant timestamps, allowing sponsors to track session completion and handle post-sponsorship actions. + type: object + properties: + api_version: + description: Data Sponsored API Version (must be 1.0.0) + type: string + enum: + - '1.0.0' + datacontenttype: + description: media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs + type: string + enum: + - 'application/json' + sponsorId: + $ref: '#/components/schemas/SponsorId' + campaignId: + $ref: '#/components/schemas/CampaignId' + sessionId: + $ref: '#/components/schemas/SessionId' + reason: + type: string + description: Reason for the termination of the sponsorship. + enum: + - EXPIRED + - TERMINATED_BY_SPONSOR + - DATA_EXHAUSTED + - USER_DEREGISTERED + - NOT_AVAILABLE + endTimestamp: + type: string + format: date-time + description: Date and time when the sponsorship session ended. + Time: + description: | + Exact time in ISO 8601 format. + 1) Date and time when the sponsorship started or when the session expires if it is still active, + 2) End date and time of the sponsorship. Calculated by adding the specified sponsorship duration to the start time (startTime).If duration is not specified, the default value defined in the onboarding campaign profile is used. + 3) End time if the session concluded due to data volume exhaustion, + 4) or when the sponsorship finished, + 5) or when the campaign started, + 6) or when the campaign expires if it is still active, + 7) or the end time if the campaign concluded due to data volume exhaustion, + 8) or when the requested action (PAUSE or RESUME) on the campaign takes effect. + 9) Start and endtime in revoke operation referes to the sponsored session revoked + type: string + format: date-time + example: "2024-08-20T14:34:56Z" + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + GENERIC_401_AUTHENTICATION_REQUIRED: + description: New authentication is needed, authentication is no longer valid + value: + status: 401 + code: AUTHENTICATION_REQUIRED + message: New authentication is required. + Generic403: + description: | + Client does not have sufficient permission. + In addition to regular scenario of `PERMISSION_DENIED`, other scenarios may exist: + - Phone number cannot be deducted from access token context.(`{"code": "INVALID_TOKEN_CONTEXT","message": "Phone number cannot be deducted from access token context"}`) + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + NOT_FOUND: + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found + DEVICE_IDENTIFIER_NOT_FOUND: + value: + status: 404 + code: DEVICE_NOT_FOUND + message: Some identifier cannot be matched to a device + Generic405: + description: Method Not Allowed + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_405_METHOD_NOT_ALLOWED: + description: Invalid HTTP verb used with a given endpoint + value: + status: 405 + code: METHOD_NOT_ALLOWED + message: The requested method is not allowed/supported on the target resource. + Generic406: + description: Not Acceptable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_406_NOT_ACCEPTABLE: + description: API Server does not accept the media type (`Accept-*` header) indicated by API client + value: + status: 406 + code: NOT_ACCEPTABLE + message: The server cannot produce a response matching the content requested by the client through `Accept-*` headers. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic415: + description: Unsupported Media Type + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_415_UNSUPPORTED_MEDIA_TYPE: + description: Payload format of the request is in an unsupported format by the Server. Should not happen + value: + status: 415 + code: UNSUPPORTED_MEDIA_TYPE + message: The server refuses to accept the request because the payload format is in an unsupported format. + Generic422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_422_DEVICE_IDENTIFIERS_MISMATCH: + description: Inconsistency between device identifiers not pointing to the same device + value: + status: 422 + code: DEVICE_IDENTIFIERS_MISMATCH + message: Provided device identifiers are not consistent. + GENERIC_422_DEVICE_NOT_APPLICABLE: + description: Service is not available for the provided device + value: + status: 422 + code: DEVICE_NOT_APPLICABLE + message: The service is not available for the provided device. + GENERIC_422_UNABLE_TO_PROVIDE_REACHABILITY_STATUS: + value: + status: 422 + code: UNABLE_TO_PROVIDE_REACHABILITY_STATUS + message: Network issue - Unable to provide reachability status + GENERIC_422_UNSUPPORTED_DEVICE_IDENTIFIERS: + value: + status: 422 + code: UNSUPPORTED_DEVICE_IDENTIFIERS + message: None of the provided device identifiers is supported by the implementation + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal Server Error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: Unknown server error. Typically a server bug. + Generic501: + description: Not Implemented + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_501_NOT_IMPLEMENTED: + description: Service not implemented. The use of this code should be avoided as far as possible to get the objective to reach aligned implementations + value: + status: 501 + code: NOT_IMPLEMENTED + message: This functionality is not implemented yet. + Generic502: + description: Bad Gateway + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_502_BAD_GATEWAY: + description: Internal routing problem in the Server side that blocks to manage the service properly + value: + status: 502 + code: BAD_GATEWAY + message: An upstream internal service cannot be reached. + Generic503: + description: Service Unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: Service Unavailable. + Generic504: + description: Gateway Timeout + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_504_TIMEOUT: + description: API Server Timeout + value: + status: 504 + code: TIMEOUT + message: Request timeout exceeded. diff --git a/original/SponsoredData/documentation/API_documentation/README.MD b/original/SponsoredData/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SponsoredData/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SponsoredData/documentation/MeetingMinutes/README.md b/original/SponsoredData/documentation/MeetingMinutes/README.md new file mode 100644 index 0000000000000000000000000000000000000000..d3f5a12faa99758192ecc4ed3fc22c9249232e86 --- /dev/null +++ b/original/SponsoredData/documentation/MeetingMinutes/README.md @@ -0,0 +1 @@ + diff --git a/original/SponsoredData/documentation/SupportingDocuments/Presentations/README.md b/original/SponsoredData/documentation/SupportingDocuments/Presentations/README.md new file mode 100644 index 0000000000000000000000000000000000000000..d3f5a12faa99758192ecc4ed3fc22c9249232e86 --- /dev/null +++ b/original/SponsoredData/documentation/SupportingDocuments/Presentations/README.md @@ -0,0 +1 @@ + diff --git a/original/SponsoredData/documentation/SupportingDocuments/README.MD b/original/SponsoredData/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SponsoredData/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/SubscriptionStatus/README.md b/original/SubscriptionStatus/README.md new file mode 100644 index 0000000000000000000000000000000000000000..88d484a6257fcb4569b444e6fdcbec0a4ab72349 --- /dev/null +++ b/original/SubscriptionStatus/README.md @@ -0,0 +1,51 @@ + + + + + + + + + +# SubscriptionStatus + +Sandbox API Repository to describe, develop, document, and test the SubscriptionStatus Service API within the Sub Project [Know Your Customer](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) of CAMARA + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/hACbBQ) + +## Scope + +* Service API “SubscriptionStatus” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* The API provides the customer with the ability to: + * obtain the current subscription status of a certain phone number, including the subscription of Voice/SMS Inbound, Voice/SMS Outbound, and Data Service Status +* Describe, develop, document, and test the APIs +* Started: August 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.2](https://github.com/camaraproject/SubscriptionStatus/releases/tag/r1.2) (Fall25), with the following API versions: + * **subscription-status v0.1.0** + [[YAML]](https://github.com/camaraproject/SubscriptionStatus/blob/r1.2/code/API_definitions/subscription-status.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/SubscriptionStatus/r1.2/code/API_definitions/subscription-status.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/SubscriptionStatus/r1.2/code/API_definitions/subscription-status.yaml) +* The latest public release is always available here: https://github.com/camaraproject/SubscriptionStatus/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/SubscriptionStatus/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/SubscriptionStatus/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of Sub Project KnowYourCustomer are held virtually + * Schedule: Bi-weekly, Tuesday, 09:00 CEST (07:00 UTC) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96235150735?password=7e3fea67-a76e-4941-8a70-392cf5545917) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/FAje) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/SubscriptionStatus/code/API_definitions/subscription-status.yaml b/original/SubscriptionStatus/code/API_definitions/subscription-status.yaml new file mode 100644 index 0000000000000000000000000000000000000000..11f73ac8c36e7b36aa9f7afed0f8db64d33b9f65 --- /dev/null +++ b/original/SubscriptionStatus/code/API_definitions/subscription-status.yaml @@ -0,0 +1,351 @@ +openapi: 3.0.3 +info: + title: SubscriptionStatus + description: | + This API allows users to obtain the current subscription status of a phone number, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + + # Introduction + + This API obtains the business subscription status of a phone number by passing it in, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + + Normally, the business subscription status is active, and the following situations may lead to abnormal business subscription status. + + **Overdue fees and downtime**: If the account balance is insufficient or the monthly rental fee is not paid on time, the operator may suspend the service. + + **Real name authentication issue**: If identity information is not updated in a timely manner (such as expired documents or incomplete second real name authentication), the operator may freeze the account. + + **Violation**: Frequent making harassing phone calls, engaging in illegal activities, and other behaviors can lead to service suspension. + + **Abnormal usage behavior**: High frequency outgoing calls, long-distance roaming, sensitive period communication, and other behaviors may be detected by the operator's risk control system, which may lead to service suspension. + + It helps verify whether telecommunication services are active or suspended for fraud prevention, customer support, and operational checks. + + **Scenario 1 - Payment System Validation**: + * A financial service provider uses this API to validate if a user's phone number has active voice/SMS services before processing high-risk transactions. If the API returns "suspended" for Voice/SMS inbound, the transaction is flagged for manual review to prevent fraud or invalid transfers. + + **Scenario 2 - Customer Service Troubleshooting**: + * The user reported that they were unable to receive calls. Customer support queries the API and identifies that "Voice/SMS inbound" is suspended. + * The user reported that they were unable to make a phone call. Customer support queries API and confirms that 'voice/SMS outbound' is suspended + * The user reported that they are unable to use the data service.Customer support queries API and confirms that 'data service status' is suspended + + The customer service personnel guides the user to reactivate the service, resolving the issue. + + # Relevant terms and definitions + - **Voice/SMS Inbound** + Indicates the ability of the subscriber to **receive** incoming voice calls and SMS messages. + - `active`: The subscriber can receive calls and SMS normally. + - `suspended`: The subscriber is blocked from receiving calls/SMS (e.g., due to account suspension). + + - **Voice/SMS Outbound** + Indicates the ability of the subscriber to **initiate** outgoing voice calls and send SMS messages. + - `active`: The subscriber can make calls and send SMS normally. + - `suspended`: The subscriber is blocked from initiating calls/SMS (e.g., due to unpaid bills or fraud restrictions). + + - **Data Service Status** + Indicates the availability and performance level of mobile data connectivity. + - `active`: Full-speed data access is enabled. + - `suspended`: Data service is completely disabled (e.g., due to contract expiration). + - `throttled`: Data service is available but speed is reduced (e.g., after exceeding usage limits). + + # Identifying the phoneNumber from the access token + + This API requires the API consumer to identify a phoneNumber as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional phoneNumber field, which therefore MUST be provided. + - When a three-legged access token is used, the subject will be uniquely identified from the access token. So, the optional phoneNumber is not used for identifying the subject, but, if it is provided in the API request body, it needs to match with the one associated with the access token. + + ## Error handling: + + - If the subject cannot be identified from the access token and the optional phoneNumber field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. This is an error typically, but not uniquely, returned in 2-legged scenarios when the access token doesn't identify a single subscription. + - If there is a mismatch between the provided phone number in the request body and the phone number associated with the access token, the server will return an error with the `403 INVALID_TOKEN_CONTEXT` error code. + + ### Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + version: 0.1.0 + + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/SubscriptionStatus +servers: + - url: "{apiRoot}/subscription-status/v0.1" + variables: + apiRoot: + default: http://localhost:9091 + description: API root defined by the provider (e.g., `api.example.com`). + +paths: + /retrive-subscription-status: + post: + security: + - openId: + - subscription-status:retrive-subscription-status + tags: + - Retrive Subscription Status + description: | + Obtain the business subscription status of the provided phone number, including Voice/SMS inbound, Voice/SMS outbound, and data service status. + operationId: retriveSubscriptionStatus + summary: Retrieve subscription status of a phone number + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionStatusRequest" + examples: + Three-Legged Without Phone Number Example: + value: {} + Two-Legged and Three-leg Access Token Example: + value: + phoneNumber: "+346661113334" + responses: + "200": + description: Subscription status retrieved successfully + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionStatusResponse" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + "422": + $ref: "#/components/responses/Generic422" + +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation ID for cross-service tracking + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + SubscriptionStatusRequest: + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + SubscriptionStatusResponse: + type: object + required: + - voiceSmsIn + - voiceSmsOut + - dataService + properties: + voiceSmsIn: + type: string + enum: [active, suspended] + description: Status of inbound Voice/SMS services + voiceSmsOut: + type: string + enum: [active, suspended] + description: Status of outbound Voice/SMS services + dataService: + type: string + enum: [active, suspended, throttled] + description: Status of mobile data service + PhoneNumber: + type: string + pattern: "^\\+[1-9][0-9]{4,14}$" + example: "+8613800138000" + description: E.164 formatted phone number + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "phoneNumber is not consistent with access token." + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token diff --git a/original/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist.md b/original/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..61cda7b625326e3f14f9452146cd547fed62deb3 --- /dev/null +++ b/original/SubscriptionStatus/documentation/API_documentation/subscription-status-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for subscription-status v0.1.0 in r1.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/subscription-status.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.1.0 | +| 5 | API documentation | M | M | M | M | Y | Embed documentation into API spec - [link](/code/subscription-status.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/subscription-status.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | Y | [link](/code/Test_definitions/subscription-status.feature) | +| 9 | Test result statement | O | O | O | M | N | To be provided | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/hACbBQ) | diff --git a/original/SubscriptionStatus/documentation/SupportingDocuments/README.MD b/original/SubscriptionStatus/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/SubscriptionStatus/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/Tenure/README.md b/original/Tenure/README.md new file mode 100644 index 0000000000000000000000000000000000000000..ae00ea7dc727e939400da5a8b9a1f9c752ec4943 --- /dev/null +++ b/original/Tenure/README.md @@ -0,0 +1,47 @@ + + + + + + + + + +# Tenure + +Sandbox API Repository to describe, develop, document, and test the Tenure Service API(s) within the Sub Project [Know Your Customer (KYC)](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/ZIDGB) + +## Scope +* Service API(s) for “Tenure” (see [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + * Establish a level of trust for a given network subscription identifier (e.g. phone number) by verifying the period of time (i.e. "tenure") for which the end user currently allocated that identifier has been associated with it by their current network operator. +* Describe, develop, document, and test the APIs +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/Tenure/releases/tag/r2.2) (Fall25), with the following API versions: + * **kyc-tenure v0.2.0** + [[YAML]](https://github.com/camaraproject/Tenure/blob/r2.2/code/API_definitions/kyc-tenure.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/Tenure/r2.2/code/API_definitions/kyc-tenure.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/Tenure/r2.2/code/API_definitions/kyc-tenure.yaml) +* The latest public release is always available here: https://github.com/camaraproject/Tenure/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/Tenure/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/Tenure/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings and minutes see [KnowYourCustomer Meetings](https://lf-camaraproject.atlassian.net/wiki/x/I4DGB) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project https://lists.camaraproject.org/g/sp-kyc + * A message to the community of this Sub Project can be sent using diff --git a/original/Tenure/code/API_definitions/kyc-tenure.yaml b/original/Tenure/code/API_definitions/kyc-tenure.yaml new file mode 100644 index 0000000000000000000000000000000000000000..ed658ca55dad80e894f92f6cc7defe58820bb4f7 --- /dev/null +++ b/original/Tenure/code/API_definitions/kyc-tenure.yaml @@ -0,0 +1,388 @@ +openapi: 3.0.3 +info: + title: KYC Tenure + description: | + # Summary + + The CAMARA Know Your Customer (KYC) Tenure API allows for verification that a network subscriber has been a customer of the Communications Service Provider (CSP) for a specified minimum length of time so as to establish a level of trust for the associated network subscription identifier. + + # API functionality + + The API defines one service endpoint: + + - `POST /check-tenure` + + Takes the network subscription identifier (e.g. the mobile phone number for a mobile network subscriber) and the specified minimum tenure date to validate for the associated network subscription. This endpoint will respond with a confirmation of whether or not the network subscriber tenure is longer than the specified date timestamp, optionally supplemented with details of the subscription contract type. + + To call this endpoint, the API consumer must first obtain a valid access token with the specified scope from the specified token endpoint, which is then passed to the endpoint via the `Authorization` header. For more details on access token processing, see below. + + ## Inputs + + The endpoint request body is a JSON object with the following parameters: + - `tenureDate`: The date from which continuous tenure of the identified network subscriber is required to be confirmed. This field is always required. + - `phoneNumber`: The network subscription identifier (i.e. the phone number of the subscriber). This field is only required if no network subscription identifier is associated with the access token. + + Note: MNOs may implement a threshold for the tenureDate aligned with their respective regulations. In that case if the tenureDate value in the request body is over the operator's threshold an error `400 OUT_OF_RANGE `is returned with an explicit message to explain the limitation. + + ## Outputs + + If successful, a JSON object is returned containing the following data: + - `tenureDateCheck`: `true` when the identified network subscription has had valid tenure since `tenureDate`, otherwise `false` + - `contractType`: The network subscription account type, if known + + An example of a JSON response object is as follows: + ``` + { + "tenureDateCheck": true, + "contractType": "PAYM" + } + ``` + + ## Errors + + If the authentication token is missing, not a valid token, or is no longer valid, a `401 UNAUTHENTICATED` error is returned + + If the API call contain a formatting or other error, a `400 INVALID_ARGUMENT` error is returned. + + If the network subscription cannot be identified from the provided parameters (e.g. the subscription identifier is not associated with any customer of the CSP), a `404 IDENTIFIER_NOT_FOUND` error is returned. + + If the API consumer has a valid access token that does not have the required scope to obtain tenure information for the specified network subscription, then a `403 PERMISSION_DENIED` error is returned. + + ### Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Identifying the phone number from the access token + + This API requires the API consumer to identify a phone number as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject will be identified from the optional `phoneNumber` field, which therefore MUST be provided. + + - When a three-legged access token is used however, this optional identifier MUST NOT be provided, as the subject will be uniquely identified from the access token. + + This approach simplifies API usage for API consumers using a three-legged access token to invoke the API by relying on the information that is associated with the access token and was identified during the authentication process. + + ## Error handling: + - If the subject cannot be identified from the access token and the optional `phoneNumber` field is not included in the request, then the server will return an error with the `422 MISSING_IDENTIFIER` error code. + + - If the subject can be identified from the access token and the optional `phoneNumber` field is also included in the request, then the server will return an error with the `422 UNNECESSARY_IDENTIFIER` error code. This will be the case even if the same phone number is identified by these two methods, as the server is unable to make this comparison. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/Tenure + +servers: + - url: "{apiRoot}/kyc-tenure/vwip" + variables: + apiRoot: + default: https://localhost:9091 + description: API root + +tags: + - name: Check Subscriber Tenure + description: Check details about the length of tenure of the subscriber + +paths: + /check-tenure: + post: + tags: + - Check Subscriber Tenure + summary: The KYC Tenure service API + description: | + Verifies a specified length of tenure, based on a provided date, for a network subscriber to establish a level of trust for the network subscription identifier. + + security: + - openId: + - kyc-tenure:check-tenure + + operationId: checkTenure + + parameters: + - in: header + name: x-correlator + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + requestBody: + required: true + content: + application/json: + schema: + $ref: "#/components/schemas/Tenure" + + responses: + "200": + description: Respond with tenure information + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/TenureInfo" + + "400": + $ref: '#/components/responses/Generic400' + "401": + $ref: '#/components/responses/Generic401' + "403": + $ref: '#/components/responses/Generic403' + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: '#/components/responses/Generic422' + + +components: + + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + + headers: + X-Correlator: + description: Correlation id for the different services + required: false + schema: + $ref: "#/components/schemas/XCorrelator" + + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: The phone number is not associated with a CSP customer account + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The phone number provided is not associated with a customer account + + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/X-Correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service is not applicable for the provided phone number + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not applicable for the provided phone number + GENERIC_422_MISSING_IDENTIFIER: + description: No phone number has been provided either explicitly or associated with the access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: No phone number has been provided + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit phone number has been provided when one is already associated with the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: An explicit phone number has been provided when one is already associated with the access token + + + schemas: + Tenure: + description: Specifies date from which continuous tenure of the identified mobile subscriber is required to be confirmed + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + tenureDate: + type: string + description: The date, in RFC 3339 / ISO 8601 compliant format "YYYY-MM-DD", from which continuous tenure of the identified network subscriber is required to be confirmed + format: date + example: "2023-07-03" + required: + - tenureDate + + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + TenureInfo: + properties: + tenureDateCheck: + description: | + `true` when the identified mobile subscription has had valid tenure since `tenureDate`, otherwise `false` + example: true + type: boolean + contractType: + description: | + If exists, populated with: + - `PAYG` - prepaid (pay-as-you-go) account + - `PAYM` - contract account + - `Business` - Business (enterprise) account + + This attribute may be omitted from the response set if the information is not available + example: "PAYM" + type: string + enum: ["PAYG", "PAYM", "Business"] + required: + - tenureDateCheck + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" diff --git a/original/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist.md b/original/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ad1d28227dbe8d5680e5f54eeab249e02b3ae5df --- /dev/null +++ b/original/Tenure/documentation/API_documentation/kyc-tenure-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API Readiness Checklist + +Checklist for kyc-tenure v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----:| +| 1 | API definition | M | M | M | M | Y | [relative link](/code/API_definitions/kyc-tenure.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | Documentation embedded within [API definition](/code/API_definitions/kyc-tenure.yaml) | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [relative link](/code/Test_definitions/kyc-tenure.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r2.2 | +| 11 | Change log updated | M | M | M | M | Y | [relative link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/wAPWB) | diff --git a/original/Tenure/documentation/SupportingDocuments/README.MD b/original/Tenure/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/Tenure/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/TrafficInfluence/README.md b/original/TrafficInfluence/README.md new file mode 100644 index 0000000000000000000000000000000000000000..53838bff705c8661a2908f562cfff9c33820a282 --- /dev/null +++ b/original/TrafficInfluence/README.md @@ -0,0 +1,53 @@ + + + + + + + + + +# TrafficInfluence + +Sandbox API Repository to describe, develop, document, and test the TrafficInfluence Service API(s) within the Sub Project [EdgeCloud](https://lf-camaraproject.atlassian.net/wiki/x/ujLe) + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/XQCbBQ) + +## Scope + +* Service API(s) “TrafficInfluence” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Influence the traffic flow from the user device toward the Edge instance of the Application providing the optimal routing. + * The traffic can be influencend even when the user device moves to a different geographical location to always get the optimal routing toward the nearer instance of an Application. +* Describe, develop, document, and test the API(s) +* Started: February 2025 (with previous work in EdgeCloud repository) + + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/TrafficInfluence/releases/tag/r1.3) (Fall25), with the following API versions: + * **traffic-influence v0.10.0** + [[YAML]](https://github.com/camaraproject/TrafficInfluence/blob/r1.3/code/API_definitions/traffic-influence.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/TrafficInfluence/r1.3/code/API_definitions/traffic-influence.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/TrafficInfluence/r1.3/code/API_definitions/traffic-influence.yaml) +* The latest public release is always available here: https://github.com/camaraproject/TrafficInfluence/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/TrafficInfluence/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/TrafficInfluence/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings of the EdgeCloud Sub Project are held virtually + * Schedule: Tuesdays 1400-1500 UTC, every two weeks (see [CAMARA Community Calendar](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) for concrete dates) + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/94237809115?password=05fb6d8a-a913-47d8-b003-db75ecdaa5d9) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/8Tve) +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/TrafficInfluence/code/API_definitions/traffic-influence.yaml b/original/TrafficInfluence/code/API_definitions/traffic-influence.yaml new file mode 100644 index 0000000000000000000000000000000000000000..ed6c7c0ba74ee9cb5c7f3dd3928b5c2c2a181bf2 --- /dev/null +++ b/original/TrafficInfluence/code/API_definitions/traffic-influence.yaml @@ -0,0 +1,1576 @@ +--- +openapi: 3.0.3 +############################################################################ +# API info # +############################################################################ +info: + title: Traffic Influence + description: | + # Overview + The reference scenario foresees a Service, composed by one or more Service + Producers deployed in different geographical locations in a distributed + Telco Edge Cloud. The Service Producer, deployed at the Edge, is referred + as Edge Application Server. + + The life cycle management of the Edge Application Server can be done with APIs, for example the CAMARA + "Edge Application Management API" under definition in the CAMARA Edge + Cloud repository (https://github.com/camaraproject/EdgeCloud). + The Telco Edge Cloud is composed by Edge Cloud Regions that contain + Edge Cloud Zones. For a more complete definition of such Telco Edge Cloud + architecture, please refer to the "Edge Application Management API" + documentation. A developer can deploy and run applications on an Edge + Cloud Zone, meaning reduced latency to end users that are nearby, as the + network path is shorter. A network operator's EdgeCloud may comprise + multiple Edge Cloud Zones, each in a discrete location to bring latency + benefits to end users across a country. + + The operator can help developers knowing which of the Edge Cloud Zones will + bring the optimal performance for a given end user and application. + + The Traffic Influence API provides the optimal routing from the + user Device (e.g. a Smartphone) to the optimal Edge Application Server instance in a specific + geographical location, installed in an Edge Cloud Zone. + + If a Service is offered by Cloud Instances and by Edge Instances, the Traffic Influence + API can be used get the optimal routing of the traffic to the Edge + Instances, maybe for a set of users. Getting the optimal routing can be + used to improve latency maybe in combination with other CAMARA APIs such as + QoD (Quality On Demand). Providing the optimal routing is indeed an + important step to get the optimal latency. + + If the Traffic Influence API is used to get the best routing at the Edge for a Device in a + geographical location and the Device moves to another geographical location, + the Traffic Influence API can be invoked to get the optimal routing in the new geographical + location for that Device. + + While the goal of the Traffic Influence API is to optimise the traffic in the mobile + network to reach the local instance of the Edge Application Server, it is a task of the + Application to generate the flow toward the expected Edge Application Server Instance. + # Introduction + The Traffic Influence API provides the capability to establish the optimal routing, in + terms of latency, in a specific geographical area, between the user Device, + e.g. the user’s smartphone, and the optimal Edge Application Server instance nearby. If the + Device moves in a different geographical location where a more suitable Edge Application Server + instance is available, the Traffic Influence API can be invoked again to influence the + Device connectivity to get the optimal routing also in the new location. + It is important to notice that the service data flow is not automatically + optimised when the user moves in a specific area, it is a task of the Traffic Influence API + Consumer to detect the changes in the Device location and to invoke the + Traffic Influence API consequently. + + The generic architecture for the Service can foresee some Cloud instances of + the Application, one or more Edge Instances of the Application. The Traffic Influence API + Consumer invokes the Traffic Influence API creating a "TrafficInfluence" resource + specifying the desired intent. + + The Traffic Influence API Producer implements the intent specified in the + "TrafficInfluence" resource. + + While the Traffic Influence API can be invoked to activate the optimal routing for any + user, it can also be used to request the optimal routing for a specific user + also specifying, as an option, a source public port and a destination public + port and protocol. Invoking the Traffic Influence API for each user, many + "TrafficInfluence" resources are created for each user to provide the + requested routing for a set of users. If the Traffic Influence API is invoked to provide + the optimal routing for any user and later it is required to provide the + optimal access only for selected users, the previous intent/resource must + be deleted. + + The same approach is used for the geographical areas where the influence + of the traffic must be applied. Invoking the Traffic Influence API without specifying a + geographical area, activates the optimal routing toward the closest Edge Application Server + instance in any geographical location. This intent must be deleted if it is + required to provide the optimal access only in selected areas. Invoking the + Traffic Influence API specifying a geographical area activates the optimal routing only if + the user is in that geographical area. The flow is optimised to reach the + Edge Application Server instance located closest to that geographical area. In a different + geographical area the user will not have the traffic flow optimised. + + To activate the optimal routing in selected geographical areas, the Traffic Influence API + must be invoked for each geographical area. Anyway it is important to + understand that the traffic optimisation strongly depends on the user's + geographical location so it is important for the Traffic Influence API Consumer to always + verify the position of the user invoking the Traffic Influence API for that user if it + moves changing its location. + The API API can also be used to optimise a specific traffic flow identified + by a source port and a destination port and protocol. To optimise the flow + from more source ports or destination ports or protocols, the Traffic Influence API must be + invoked many times. + + It is important to notice that it is a task of the Client Application to + use the most adequate means to send the application flow to the right + server (Edge Application Server), for example using Edge DNS or using the target Edge Application Server IP address. + The Traffic Influence API provides back the selected Edge Application Server instance identifier from which the + Client Application can retrieve the destination IP address of its backed + server, to properly configure the service data flow. + + The Traffic Influence API can be used to: + - optimise the routing when Devices need to consume the service provided + by a local Edge Application Server Instances. + - affect an already established Device routing when the Device moves + among different geographical locations. When the Traffic Influence API consumer detects + a Device has entered a geographical location where an Edge Application Server instance is + available, it can invoke the Traffic Influence API to get the optimal routing toward + that Edge Application Server instance. + If the Device moves to another geographical location, served by another + Edge Application Server instance, the routing might not be optimal any more. In the case the + Application detects a location change, it can invoke the Traffic Influence API again to + request a new routing optimization toward the new Edge Application Server instance. + ## Quick Start + The Traffic Influence API is consumed by an Application Function (AF) requesting for the + optimal routing, in term of latency, for the traffic flow from a Device + toward Edge Application Server instances in Edge Cloud Zones. + + When the Application (the Edge Application Server) is onboarded and deployed in the Edge Cloud + Zones, the Application is identified with a unique identifier ("appId"). + + Using the application identifier ("appId") and specifying a Zone or a Region + the Telco Operator Platform, autonomously identifies the best instance of + the Edge Application Server toward which routing the traffic flow and configures the Mobile + Network accordingly to get the fastest routing. + + If just the application identifier is used, the Telco Operator Platform + identifies all the Edge Application Server Instances and activates the optimal routing on the + Mobile Network. + + If the optimal routing in term of latency should be available just for a set + of users, the Traffic Influence API must be invoked for each user creating a new + TrafficInfluce resource for each one. + If the Application offers different services on different interfaces a + traffic filter based on IP, Port and Protocol can be used. I this way it is + also possible to redirect different users to different interfaces. + Here are some possible intents: + 1) activate the optimal routing for the closest Edge Application Server instance: the Traffic Influence API + must be invoked with the "appId". The Telco Operator Platform identifies + all the Edge Application Server instances and activates the optimal routing on the Mobile + Network so that the user is connect to the closest Edge Application Server instance. + 2) activate the optimal routing in a specific Region or Zone: the Traffic Influence API + must be invoked with the "appId" and the Zones and Regions identifiers. + 3) activate the optimal routing for a user Device: the Traffic Influence API can be + invoked with a user Device identifier (“Device”). For each user Device, + a Traffic Influence API invocation is required. The optimal routing is provided only for + the requested Devices. + # API Documentation + The usage of the Traffic Influence API is based on the management of a "TrafficInfluence" + resource, an object containing the intent requested invoking the Traffic Influence API and + that is implemented by the platform configuring the Mobile Network for the + optimal routing toward the Edge Application Server instance. + + The "TrafficInfluence" resource can be created (providing the related + parameters that specify the desired intent), queried, modified and + deleted. + + The Traffic Influence API is asynchronous, a notification is available providing + information about the status of the requested resource. + For an Application (identified by "appId") many "TrafficInfluence" resources + can be created, e.g. to add multiple users, regions or zones. + + When an intent is expressed and a resource have been created, if the intent + must be modified, it is suggested to use the PATCH method + (/traffic-influeces/{trafficInfluenceID}). Anyway, any other new intent + (e.g. for the same device) will override the previous ones. + + Before starting to use the Traffic Influence API, the developer needs to know about the + below specified details: + + **TrafficInfluence:** + This object represents the resource that carries the requirements from the + user to be implemented. The Traffic Influence API is invoked for the life cycle management + of this resource (CRUD). The resource contains the intents from the Traffic Influence API + Consumer. Managing this resource, the developer can specify in which + geographical location the routing must be applied, toward which application, + maybe for a specific set of users or for a limited period of time. + + **trafficInfluenceID:** + Identifier for the Traffic Influence resource. This parameter is returned + by the Traffic Influence API and must be used to update it (e.g., adding a Device or + deleting it). A different Traffic Influence resource must be created for + any Device or Zone or Region. All these resources are related to an + Application identified by "appId". + + **apiConsumerId:** + Unique identifier for the Traffic Influence API Consumer. + + **edgeCloudRegion:** + The Developer can specify in which geographical area he requires the optimal + routing toward application instances running there. An Edge Cloud Region is + equivalent to a Region on a Public Cloud. The higher construct in the + hierarchy exposed to an Application Provider who wishes to deploy an + Application on the Edge Cloud and broadly represents a geography. + An Edge Cloud Region typically contains one or multiple Edge Cloud Zones. + The Edge Cloud Region name is provided by the Telco Operator and can also be + used or retrieved with other CAMARA APIs (e.g. “Edge Application Management + API”). To add more regions the Traffic Influence API must be invoked (POST) for each + "region". If in a "region" there are many Application instances active in + different "zones", the Traffic Influence API can be invoked to configure the optimal + routing for all the instances with just one API call specifying the + "region". + + If just the Application instances in some Edge Cloud Zone must be affected, + the Traffic Influence API can be invoked for the zones of interest, without specifying + the "region" in the API call. If just some specific Application instance + must be affected, it is not required to specify any "region" or "zone", + and the parameter "appInstanceId" can be used. + + **edgeCloudZoneId:** + An Edge Cloud Zone is the lowest level of abstraction exposed to an + Application Provider who wants to deploy an Application on Edge Cloud. + Edge Cloud Zones exists within a Edge Cloud Region. + + To add more "zones" the Traffic Influence API must be invoked (POST) for each "zone". + + **appId:** + A globally unique identifier associated with the application. This + identifier is provided during the application onboarding process. + To influence the traffic toward a specific Application. It is the Operator + Platform that detects the appropriate Application instance in the selected + "region" or "zone". + + **appInstanceId:** + A globally unique identifier generated by the Operator Platform to identify + a specific instance of the Application in a specific zone. To influence a + traffic toward a specific Application instance. If just some specific + Application instance must be affected, it is not required to specify any + "region" or "zone", the parameter "appInstanceId" can be used. + The value for appInstanceId can be retrieved using the CAMARA API + Edge Application Management, included in the Edge Cloud API Family. + + **sourceTrafficFilters:** + The traffic can be from a specific public port in the device. If this + parameter is used, the influenced flow is from the public port defined in + "sourceTrafficFilters" rather than the public port specified in "Device" + + **destinationTrafficFilters:** + The Application can expose different service on different interfaces, + identified by port and protocol, with this parameter it is possible to + route the traffic toward a specific port and protocol exposed by the + Application. + + **Device:** + An user Device can be provided as an input. The Device can be identified by + the phone number (phoneNumber) or by its IP Address (Ipv4Address, + Ipv6Address) also specifying a Port. For IP address both the private (as + seen from inside the Device) and the public (as seen over Internet by a + server connected to the Device) can be used. To add more users the Traffic Influence API + must be invoked (POST) of each user Device. New "TrafficInfluence" + resources are created (with different "trafficInfluenceID"). The routing + toward the selected Application instance is only applied for provided user + Devices. "publicPort" can be used to identify the device. "publicPort" can + be also used to identify the flow to be influenced. If the flow to be + influenced is from a different public port, "sourceTrafficFilters" can be + used. If more than one Device identifier is provided only one will be used + by the Traffic Influence API to perform the network optimization. The one used is + returned in the notification callback. + + **Notification:** + Developers can specify a callback URL on which notifications + regarding the requested intent can be received. The notification will be + sent as a CloudEvent compliant message. For example to be notified when the + requested optimal routing is active. It is also provided back the + identifier for the selected Edge Application Server instance ("selected_appInstanceId") + from which the Client Application can retrieve the destination IP address of + its back-end server, to properly configure the service data flow. This + information can be retrieved using the APIs, for example the Edge Application Management under development in CAMARA. + # Authorization and authentication + The "Camara Security and Interoperability Profile" provides details of how + an API consumer requests an access token. Please refer to Identity and + Consent Management + (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during + the onboarding process, happening between the provider of the application + consuming the API and the operator's API exposure platform, taking into + account the declared purpose for accessing the API, whilst also being + subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can + exercise their rights through mechanisms such as opt-in and/or opt-out, + the use of three-legged access tokens is mandatory. This ensures that + the API remains in compliance with privacy regulations, upholding the + principles of transparency and user-centric privacy-by-design. + # Identifying the phone number from the access token + This API optionally requires the API consumer to identify a phone number + as the subject of the API as follows: + - When the API is invoked using a two-legged access token, the subject + will be identified from the optional `device` object field, which + therefore MUST be provided. + - When a three-legged access token is used however, this optional + identifier MUST NOT be provided, as the subject will be uniquely + identified from the access token. + + This approach simplifies API usage for API consumers using a + three-legged access token to invoke the API by relying on the + information that is associated with the access token and was + identified during the authentication process. + ## Error handling: + - If the subject cannot be identified from the access token and the + optional `device` object field is not included in the request, then + the server will return an error with the + `422 MISSING_IDENTIFIER` error code. + - If the subject can be identified from the access token and the + optional `device` object field is also included in the request, then + the server will return an error with the `422 UNNECESSARY_IDENTIFIER` + error code. This will be the case even if the same device is + identified by these two methods, as the server is unable to make + this comparison. + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. + The applicable Commonalities Release can be identified in the + `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + # FAQ's + (FAQs will be added in a later version of the documentation) + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Product documentation at Camara + url: https://github.com/camaraproject/TrafficInfluence +############################################################################ +# Servers # +############################################################################ +servers: + - url: "{apiRoot}/traffic-influence/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root for the Traffic Influence API +############################################################################ +# Tags # +############################################################################ +tags: + - name: Traffic Influence API read + description: Reads existing TrafficInfluence resources + - name: Traffic Influence API write + description: Creates of modifies a TrafficInfluence resource +############################################################################ +# Paths # +############################################################################ +paths: + /traffic-influences: + get: + security: + - openId: + - 'traffic-influence:traffic-influences:read' + parameters: + - $ref: '#/components/parameters/x-correlator' + - in: query + name: appId + schema: + $ref: "#/components/schemas/AppId" + description: Used to select traffic influence resources filtered by + appId. For privacy reasons, if a resource is related to a user, the + parameter Device is not returned. + tags: + - Traffic Influence API read + summary: Retries existing TrafficInfluence Resources + description: Reads all of the active TrafficInfluence resources owned by + the same API Consumer + operationId: getAllTrafficInfluences + responses: + '200': + description: Returns the information about existing TrafficInfluence + resources. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + type: array + items: + $ref: "#/components/schemas/TrafficInfluence" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "429": + $ref: "#/components/responses/Generic429" + post: + tags: + - Traffic Influence API write + summary: Creates a new TrafficInfluence resource influencing the + traffic toward local instances of the Application for any user. + description: Takes as input an object containing the intents from the API + Consumer and creates a TrafficInfluence resource accordingly. The + trafficInfluenceID parameter, that is part of the object, must not be + valorized when creating a new resource. For this reason the + trafficInfluenceID parameter must be avoided in the object, anyway it + will be ignored by the API Producer. It is automatically generated by + the system and returned in the response. + operationId: postTrafficInfluence + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:write' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PostTrafficInfluence' + responses: + '201': + description: TrafficInfluence resource created, the related object is + returned with the resource ID (trafficInfluenceID) and status (state) + valorised. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "409": + $ref: "#/components/responses/Generic409" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + /traffic-influence-devices: + post: + tags: + - Traffic Influence API write + summary: Creates a new TrafficInfluence resource influencing the + traffic toward local instances of the Application for a specific user. + description: Takes as input an object containing the intents from the API + Consumer and creates a TrafficInfluence resource accordingly. The + trafficInfluenceID parameter, that is part of the object, must not be + valorized when creating a new resource. For this reason the + trafficInfluenceID parameter must be avoided in the object, anyway it + will be ignored by the API Producer. It is automatically generated by + the system and returned in the response. + operationId: postTrafficInfluenceDevice + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influence-devices:write' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PostTrafficInfluenceDevice' + responses: + '201': + description: TrafficInfluence resource created, the related object is + returned with the resource ID (trafficInfluenceID) and status (state) + valorised. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + /traffic-influences/{trafficInfluenceID}: + parameters: + - name: trafficInfluenceID + in: path + description: Identifier of the specific TrafficInfluence resource to be + retrieved, modified or deleted. It is the value used to fill + trafficInfluenceID parameter. + required: true + schema: + type: string + get: + tags: + - Traffic Influence API read + summary: Reads a specific TrafficInfluence resource identified by the + trafficInfluenceID value. + description: Returns a specific TrafficInfluence resources owned by the + same API Consumer. For privacy reasons, if a resource is related to a + user, the parameter Device is not exchanged. + operationId: getTrafficInfluenceById + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:read' + responses: + '200': + description: OK. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + patch: + tags: + - Traffic Influence API write + summary: updates a specific TrafficInfluence resource, identified by the + trafficInfluenceID value. If used for a specific user, the Device + parameter can not be modified. + description: The resource identified by the trafficInfluenceID value can + be modified. Before the PATCH can be invoked the status (state) of the + resource must be "active". If not an error code 409 (DENIED_WAIT) is + returned. + operationId: patchTrafficInfluence + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - 'traffic-influence:traffic-influences:update' + requestBody: + description: Describes the request body + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/PatchTrafficInfluence' + responses: + '200': + description: TrafficInfluence resource edited, the related object is + returned, the status (state) is updated. + content: + application/json: + schema: + $ref: '#/components/schemas/TrafficInfluence' + headers: + Location: + description: Link to the created traffic influence resource + schema: + type: string + description: Link to the created traffic influence resource + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" + delete: + tags: + - Traffic Influence API write + summary: Delete an existing TrafficInfluence resource + description: invoked by the API Consumer to stop influencing the traffic, + deleting a TrafficInfluence resource previously created. The notification + will be sent via Cloud Event with the information already available in + the TrafficInfluence resource identified by "trafficInfluenceID". + operationId: deleteTrafficInfluence + security: + - openId: + - 'traffic-influence:traffic-influences:delete' + parameters: + - $ref: '#/components/parameters/x-correlator' + responses: + '202': + description: Deletion in progress. + resources. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: '#/components/responses/Generic404' + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/Generic422" + "429": + $ref: "#/components/responses/Generic429" + callbacks: + onTrafficInfluenceChanged: + $ref: "#/components/callbacks/onTrafficInfluenceChanged" +############################################################################ +# Components # +############################################################################ +components: + securitySchemes: + openId: + description: to support both Consent Management, via 3-legged authentication, + when sensitive data are exchanged and OAuth2, 2-legged authentication, + for endpoints not exchanging sensitive data. + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + description: Bearer authentication for notifications + type: http + scheme: bearer + bearerFormat: "{$request.body#sinkCredential.credentialType}" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services. + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + ######################################################################### + # Events/Callbacks # + ######################################################################### + callbacks: + onTrafficInfluenceChanged: + # when data is sent, it will be sent to the callback url provided + '{$request.body.subscriptionRequest.sink}': + post: + tags: + - Traffic Influence CALLBACK Operation + summary: Provides a notifican channel for changes in the + TrafficInfluence resource + description: Creating, modifying or delating a Traffic Influece + resourece is an asycronous task. For this reason a notification + channel via callback to a specified URL is provided. + operationId: trafficInfluenceCloudEvent + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - notificationsBearerAuth: [] + requestBody: + description: subscription payload which contains the updated + traffic influence instance + content: + application/cloudevents+json: + schema: + $ref: '#/components/schemas/CloudEvent' + example: + id: "string" + source: "https://notificationSendServer12.example.com" + specversion: "1.0" + datacontenttype: "application/json" + type: "org.camaraproject.traffic-influence.v1.traffic-influence-change" + data: + selected_appInstanceId: + - "3fa85f64-5717-4562-b3fc-2c963f66afa6" + deviceResponse: + phoneNumber: "+123456789" + time: "2018-04-05T17:31:00Z" + responses: + '202': + description: Your server implementation should return this HTTP + status code if the data was received successfully + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '204': + description: Your server should return this HTTP status code if + no longer interested in further updates + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + '401': + description: Your server should return this HTTP status code if + the request can not be authenticated due to missing, invalid, + or expired credentials. A new authentication is required. + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + ########################################################################## + # Resources # + ########################################################################## + schemas: + TrafficInfluence: + description: Resource conteining the informations to influence the + traffic toward local instances of the Application, for any user. + type: object + properties: + trafficInfluenceID: + type: string + description: Identifier for the Traffic Influence resource. This + parameter is returned by the API and it is used to update it + (e.g., modify or delete the TrafficInfluence resource). + apiConsumerId: + type: string + description: Unique Identifier of the Traffic Influence API Consumer. + appId: + $ref: '#/components/schemas/AppId' + appInstanceId: + $ref: '#/components/schemas/AppInstanceId' + edgeCloudRegion: + $ref: '#/components/schemas/EdgeCloudRegion' + edgeCloudZoneId: + $ref: '#/components/schemas/EdgeCloudZoneId' + state: + type: string + description: it reports the state of the TrafficInfluence resource. + When first invoked, the resource is 'ordered'. When the platforms + prepares the resource, it is 'created'. When the new routing is + enabled in the network, the state is 'active'. If an error occurs + in the resource creation or in its activation, the state is 'error'. + When the DELETE method is invoked the state is + 'deletion in progress'. + After the resource is deleted (as a consequence of the previous + invocation of the DELETE method) the state is 'deleted'. + enum: + - 'ordered' + - 'created' + - 'active' + - 'error' + - 'deletion in progress' + - 'deleted' + sourceTrafficFilters: + description: Public source port used by the device for flows to which + the requested traffic influence should apply. Traffic influence will + be applied to the flow between "sourcePort" and the Application + Server address and port specified in "destinationTrafficFilters". + type: object + properties: + sourcePort: + allOf: + - $ref: "#/components/schemas/Port" + destinationTrafficFilters: + description: Identifies the destination IP packet filters. To be + used when it is needed a traffic flow towards a specific Edge Application Server + interface identified by a protocol and a port. Also the Protocol + (e.g. TCP or UDP) can be specified. + type: object + properties: + destinationPort: + allOf: + - $ref: "#/components/schemas/Port" + destinationProtocol: + allOf: + - $ref: "#/components/schemas/Protocol" + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + required: + - apiConsumerId + - appId + PostTrafficInfluence: + description: inherits from TrafficInfluence restricting the access + (readonly) to "trafficInfluenceID" and "state", to be used by the API + Consumer to create a TrafficInfluece resource for any user. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + trafficInfluenceID: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + PostTrafficInfluenceDevice: + description: inherits from TrafficInfluence restricting the access + (read-only) to "trafficInfluenceID" and "state", to be used by the API + Consumer to create a TrafficInfluece resource for a specific user. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + device: + $ref: '#/components/schemas/Device' + trafficInfluenceID: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + PatchTrafficInfluence: + description: inherits from TrafficInfluence and restricts the access to + certain parameters. + Only some parameter can be indeed modified with the PATCH operation. + allOf: + - $ref: "#/components/schemas/TrafficInfluence" + properties: + trafficInfluenceID: + readOnly: true + apiConsumerId: + readOnly: true + appId: + readOnly: true + state: + readOnly: true + subscriptionRequest: + $ref: '#/components/schemas/SubscriptionRequest' + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the + source context. + minLength: 1 + source: + $ref: '#/components/schemas/Source' + type: + $ref: "#/components/schemas/EventTypeNotification" + specversion: + type: string + description: Version of the specification to which this event conforms + (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, + must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: Event details payload described in each CAMARA API and + referenced by its type + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.traffic-influence.v1.traffic-influence-change: "#/components/schemas/TrafficInfluenceNotification" + TrafficInfluenceNotification: + type: object + description: Notification channel for changes in the TrafficInfluence + resource. It returns back the TrafficInfluence resource with the + updated status ("state"). It provides back the identifiers + of the selected Edge Application Server instances. If more than one Device identifier was + provided, just the one used by the Traffic Influence API is returned. + allOf: + - $ref: "#/components/schemas/PostTrafficInfluenceDevice" + properties: + selected_appInstanceId: + type: array + items: + $ref: '#/components/schemas/AppInstanceId' + deviceResponse: + $ref: "#/components/schemas/DeviceResponse" + DateTime: + type: string + format: date-time + description: | + Timestamp of when the occurrence happened. Must adhere to RFC 3339. + WARN: This optional field in CloudEvents specification is required + in CAMARA APIs implementation. + example: '2018-04-05T17:31:00Z' + Source: + type: string + format: uri-reference + minLength: 1 + description: | + Identifies the context in which an event happened - be a non-empty + `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.example.com" + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/SubscriptionProtocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: | + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + MQTT3: "#/components/schemas/MQTTSubscriptionRequest" + MQTT5: "#/components/schemas/MQTTSubscriptionRequest" + AMQP: "#/components/schemas/AMQPSubscriptionRequest" + NATS: "#/components/schemas/NATSSubscriptionRequest" + KAFKA: "#/components/schemas/ApacheKafkaSubscriptionRequest" + SubscriptionProtocol: + type: string + enum: ["HTTP", "MQTT3", "MQTT5", "AMQP", "NATS", "KAFKA"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + Config: + description: | + Implementation-specific configuration parameters needed by the subscription manager for acquiring events. + In CAMARA we have predefined attributes like `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` + Specific event type attributes must be defined in `subscriptionDetail` + Note: if a request is performed for several event type, all subscribed event will use same `config` parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/CreateSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: The subscription expiration time (in date-time format) requested by the API consumer. It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. Up to API project decision to keep it. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: | + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + example: + credentialType: ACCESSTOKEN + properties: + credentialType: + type: string + enum: + - PLAIN + - ACCESSTOKEN + - REFRESHTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + PLAIN: "#/components/schemas/PlainCredential" + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + REFRESHTOKEN: "#/components/schemas/RefreshTokenCredential" + required: + - credentialType + PlainCredential: + type: object + description: A plain credential as a combination of an identifier and a secret. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + required: + - identifier + - secret + properties: + identifier: + description: The identifier might be an account or username. + type: string + secret: + description: The secret might be a password or passphrase. + type: string + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + RefreshTokenCredential: + type: object + description: An access token credential with a refresh token. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + refreshToken: + description: REQUIRED. An refresh token credential used to acquire access tokens. + type: string + refreshTokenEndpoint: + type: string + format: uri + description: REQUIRED. A URL at which the refresh token can be traded for an access token. + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + - refreshToken + - refreshTokenEndpoint + CreateSubscriptionDetail: + description: The detail of the requested event subscription. + type: object + EventTypeNotification: + type: string + description: Event triggered when an event-type event occurred. + enum: + - org.camaraproject.traffic-influence.v1.traffic-influence-change + SubscriptionEventType: + type: string + description: | + event-type that could be subscribed through this subscription. Several event-type could be defined. + enum: + - org.camaraproject.traffic-influence.v1.traffic-influence-change + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + ######################################################################## + # Types # + ######################################################################## + EdgeCloudZoneId: + type: string + format: uuid + description: | + Unique identifier created by the Edge Cloud Platform to identify an + Edge Cloud Zone within an Edge Cloud + EdgeCloudRegion: + type: string + description: | + Human readable name of the geographical Edge Cloud Region of + the Edge Cloud. Defined by the Edge Cloud Provider. + additionalProperties: false + Device: + description: | + End-user equipment able to connect to a mobile network. Examples of + devices include smartphones or IoT sensors/actuators. + The developer can choose to provide the below specified device + identifiers: + * `ipv4Address` + * `ipv6Address` + * `phoneNumber` + * `networkAccessIdentifier` + NOTE1: the MNO might support only a subset of these options. + The API invoker can provide multiple identifiers to be compatible + across different MNOs. In this case the identifiers MUST belong to + the same device. + NOTE2: as for this Commonalities release, we are enforcing that the + networkAccessIdentifier is only part of the schema for + future-proofing, and CAMARA does not currently allow its use. + After the CAMARA meta-release work is concluded and the relevant + issues are resolved, its use will need to be explicitly documented + in the guidelines. + type: object + properties: + phoneNumber: + $ref: "#/components/schemas/PhoneNumber" + networkAccessIdentifier: + $ref: "#/components/schemas/NetworkAccessIdentifier" + ipv4Address: + $ref: "#/components/schemas/DeviceIpv4Addr" + ipv6Address: + $ref: "#/components/schemas/DeviceIpv6Address" + minProperties: 1 + PhoneNumber: + description: A public identifier addressing a telephone subscription. In + mobile networks it corresponds to the MSISDN (Mobile Station + International Subscriber Directory Number). In order to be globally + unique it has to be formatted in international format, according to + E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + NetworkAccessIdentifier: + description: A public identifier addressing a subscription in a mobile + network. In 3GPP terminology, it corresponds to the GPSI formatted with + the External Identifier ({Local Identifier}@{Domain Identifier}). + Unlike the telephone number, the network access identifier is not + subjected to portability ruling in force, and is individually managed + by each operator. + type: string + example: "123456789@domain.com" + DeviceIpv4Addr: + type: object + description: | + The device should be identified by either the public (observed) IP + address and port as seen by the application server, or the private + (local) and any public (observed) IP addresses in use by the device + (this information can be obtained by various means, for example from + some DNS servers). + If the allocated and observed IP addresses are the same (i.e. NAT is not + in use) then the same address should be specified for both + publicAddress and privateAddress. + If NAT64 is in use, the device should be identified by its publicAddress + and publicPort, or separately by its allocated IPv6 address (field + ipv6Address of the Device object) + In all cases, publicAddress must be specified, along with at least one + of either privateAddress or publicPort, dependent upon which is known. + In general, mobile devices cannot be identified by their public IPv4 + address alone. + properties: + publicAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + privateAddress: + $ref: "#/components/schemas/SingleIpv4Addr" + publicPort: + $ref: "#/components/schemas/Port" + anyOf: + - required: [publicAddress, privateAddress] + - required: [publicAddress, publicPort] + example: + publicAddress: "84.125.93.10" + publicPort: 59765 + SingleIpv4Addr: + description: A single IPv4 address with no subnet mask + type: string + format: ipv4 + example: "84.125.93.10" + Port: + description: TCP or UDP port number + type: integer + minimum: 0 + maximum: 65535 + Protocol: + description: The protocol for the influenced flow. It can be specified and + it is identified by a string according to the column “Keyword” as defined + by IANA (https://www.iana.org/assignments/protocol-numbers/\ + protocol-numbers.xhtml), e.g. UDP or TCP. + type: string + example: "TCP" + DeviceIpv6Address: + description: | + The device should be identified by the observed IPv6 address, or by any + single IPv6 address from within the subnet allocated to the device + (e.g. adding ::0 to the /64 prefix). + type: string + format: ipv6 + example: 2001:db8:85a3:8d3:1319:8a2e:370:7344 + DeviceResponse: + description: | + An identifier for the end-user equipment able to connect to the network + that the response refers to. This parameter is only returned when the + API consumer includes the `device` parameter in their request (i.e. + they are using a two-legged access token), and is relevant when more + than one device identifier is specified, as only one of those device + identifiers is allowed in the response. + If the API consumer provides more than one device identifier in their + request, and this schema is included in the response definition, the API provider MUST use it to return a single identifier which is the + one they are using to fulfil the request, even if the identifiers do not + match the same device. API provider does not perform any logic to + validate/correlate that the indicated device identifiers match the same + device. No error should be returned if the identifiers are otherwise + valid to prevent API consumers correlating different identifiers with a + given end user. + allOf: + - $ref: "#/components/schemas/Device" + - maxProperties: 1 + AppInstanceId: + type: string + format: uuid + description: A globally unique identifier associated with a running + instance of an application. OP generates this identifier. + AppId: + type: string + format: uuid + example: "6B29FC40-CA47-1067-B31D-00DD010662DA" + description: A globally unique identifier associated with the application. + OP generates this identifier when the application is submitted over NBI. + ######################################################################## + # Responses # + ######################################################################## + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or + query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a + given field has has an unsupported value. + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication + is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired + credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have + the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform + this action. + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: The Traffic Influence resource identifier is unknown. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + - CONFLICT + - DENIED_WAIT + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + GENERIC_409_CONFLICT: + description: Duplication of an existing resource + value: + status: 409 + code: CONFLICT + message: A specified resource duplicate entry found. + GENERIC_409_DENIED_WAIT: + description: Patch denial if the previous intent is not yet + fulfilled + value: + status: 409 + code: DENIED_WAIT + message: It is not possible to modify the Traffic Influence + resource because it is still under provisioning. The resource + can be modified when it is fully implemented and activated. + Please wait for the resource status (state) to be "active" + before trying to update it. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + Generic422: + description: Unprocessable Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNNECESSARY_IDENTIFIER + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided + identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the + provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the + request and the device or phone number identification + cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The phone number cannot be identified. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when + a device or phone number has already been identified + from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The phone number is already identified by the + access token. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. diff --git a/original/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist.md b/original/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..967cc25183671d30ece0538a2fee6ad54fa14fb5 --- /dev/null +++ b/original/TrafficInfluence/documentation/API_documentation/traffic-influence-API-Readiness-Checklist.md @@ -0,0 +1,33 @@ +# API Readiness Checklist + +Checklist for traffic-influence v0.10.0 in r.1.3 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:----| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/traffic-influence.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | v0.10.0 | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [link](/documentation/API_documentation/traffic-influence-user-story-use-case-1.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [Device](/code/Test_definitions/traffic-influence-postTrafficInfluenceDevice.feature), [Every User](/code/Test_definitions/traffic-influence-postTrafficInfluence.feature) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public-release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/d4JlBQ) | + + + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). + + diff --git a/original/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1.md b/original/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1.md new file mode 100644 index 0000000000000000000000000000000000000000..805815c8969d0542842a67ecd074286c08b6f852 --- /dev/null +++ b/original/TrafficInfluence/documentation/API_documentation/traffic-influence-user-story-use-case-1.md @@ -0,0 +1,16 @@ +| Item | Description | Support Qualifier | +|----|----|----| +|Summary|A Service is provided by a Cloud instances of an Application. In a specific geographical area, the Service must be provided by an edge instance of the Application (EAS) for Premium users. The Application Function (AF) of the Service invokes the Traffic Influence API (exposed by the OP) to activate the appropriate routing at the Edge of the mobile network toward the local EAS Instance for the Premium Users. Premium Users access the service in that geographical area with the best user experience while Free users get a best effort service provided by the Cloud instances of the Service.| M | +|Roles, Actor(s) and scope|Application Function: role of Traffic Influence API consumer
                                                                                Operator Platform: role of Traffic Influence API provider
                                                                                User Equipment: role of Service consumer
                                                                                Edge Application Server: role of Service producer

                                                                                Scope: B2B use case to activate a specific traffic flow at the Edge toward an existing EAS in the Edge datacenters| M | +|NF Requirements|| O | +|Pre-conditions|• The EAS is deployed in the Edge datacenter
                                                                                • A connectivity between the Telco Edges (where the UPF is located) and the Edge datacenter (where the EAS Instance is located) is in place.| M | +|Begins when|The AF invokes the Traffic Influence API to have the fastest routing toward a specific EAS Instance.| M | +|Step 1|The OP authorizes the request (terminates with a notification to the AF if it is not valid)| M | +|Step 2|The Traffic Influence API Producer validates the request (terminates with a notification to the AF if it is not coherent with the policies)| M| +|Step 3|The API Producer checks for network resources to implement the request (terminates with a notification to the AF if not available)| M | +|Step 4|The API Producer configures the network resources to get the fastest routing toward the requested EAS Instance| M | +|Step 5|The API Producer notifies the AF that the requested routing has been activated. The API Producer returns and Identifier for the created resource| M | +|Step 6|The AF invokes the TI API as many times according to the number of users to be added to the resource (passing the resource identifier) (the cycle goes through Steps 2-3-4-5 each time)| M | +|Ends when|All the users are properly configured| M | +|Post-conditions|The traffic flow is routed from the selected UPF to the requested EAS Instance for the selected users| M | +|Exceptions|Step 4 can generate an exception to be notified to the AF| M | \ No newline at end of file diff --git a/original/TrafficInfluence/documentation/SupportingDocuments/README.MD b/original/TrafficInfluence/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/TrafficInfluence/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/VerifiedCaller/README.md b/original/VerifiedCaller/README.md new file mode 100644 index 0000000000000000000000000000000000000000..1cab89012bf1ed22a76f43fde247105a3a847be4 --- /dev/null +++ b/original/VerifiedCaller/README.md @@ -0,0 +1,57 @@ + + + + + + + + + +# VerifiedCaller + +Sandbox API Repository to describe, develop, document, and test the VerifiedCaller Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/Pive) + +## Scope + +* Service APIs to deliver secure and branded calls (see “VerifiedCaller” within [APIBacklog.md](https://github.com/camaraproject/APIBacklog/blob/main/documentation/APIbacklog.md)) +* It provides the API consumer with the ability to: + * Announce a branded call via the Verified Caller API + * Register the content via Service Registration + * NOTE: The scope of these APIs should be limited (at least at the first stage) to calls made over 4G or 5G. +* Describe, develop, document, and test the APIs +* Started: May 2024 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r1.3](https://github.com/camaraproject/VerifiedCaller/releases/tag/r1.3) (Fall25), with the following API versions: + * **brand-registration v0.1.0** + [[YAML]](https://github.com/camaraproject/VerifiedCaller/blob/r1.3/code/API_definitions/brand-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/brand-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/brand-registration.yaml) + * **verified-caller v0.1.0** + [[YAML]](https://github.com/camaraproject/VerifiedCaller/blob/r1.3/code/API_definitions/verified-caller.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/verified-caller.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/VerifiedCaller/r1.3/code/API_definitions/verified-caller.yaml) +* The latest public release is always available here: https://github.com/camaraproject/VerifiedCaller/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/VerifiedCaller/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/VerifiedCaller/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## Contributing +* Meetings + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/95553339882?password=c2022918-91d5-4d3d-9c4f-14b759b16e69) + * Schedule: bi-weekly (odd weeks), Thursday, 10:00 AM UTC (11:00 AM CET) + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/l/cp/1k9fcyv1) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . diff --git a/original/VerifiedCaller/code/API_definitions/brand-registration.yaml b/original/VerifiedCaller/code/API_definitions/brand-registration.yaml new file mode 100644 index 0000000000000000000000000000000000000000..fba9b93e42f5ab1280ebe0c242caf81753551675 --- /dev/null +++ b/original/VerifiedCaller/code/API_definitions/brand-registration.yaml @@ -0,0 +1,896 @@ +openapi: 3.0.3 +info: + title: Brand Registration + description: | + This API provides the ability to associate a calling party number with a human-readable string that is displayed to the callee on their device screen instead of the calling number. + + # Introduction + + Consumers of this API can associate calling party numbers with a human-readable string that is to be displayed to the callee on their device screen instead of the calling number. This allows the callee to recognize the caller even if the calling party number is not registered in the callee's device and increases the likelihood of the call being answered. + + Brand Registration API could be useful in scenarios such as: + - Telesales + - Customer Support + - Outreach efforts of NGOs. + - Calls placed by authorities or government institutions for official matters. + + # Relevant terms and definitions + * **phoneNumber** and **phoneNumberAlternate**: A pair of E.164 numbers representing the caller. Depending on the caller's networks access setup , only phoneNumber or both phoneNumber & phoneNumberAlternate may be used to uniquely identify the caller. The values typically correspond to parameters used in telecom signalling protocols, e.g. PAI and FROM headers in SIP. + * **displayName**: A human-readable string that is to be displayed to the callee on their device screen instead of the calling number. + * **displayAsset**: A visual asset (e.g. a logo, image or video) that is to be displayed to the callee on their device screen instead of the calling number. Support of the visual asset depends on the service provider and callee's device. If the service provider does not support the parameter, it SHALL clearly document the limitation and SHOULD silently ignore the parameter if received. + * **customerId** : A string to represent the owner of the displayName, e.g. a commercial brand or an institution. + * **verifyCallerAction**: An instruction applied during actual call setup. Indicates the action to be taken by the service provider if the authenticity of the caller cannot be established using VerifiedCaller API capabilities. + # API Functionality + + The API exposes the following endpoints/operations: + + - `/registrations` : + - **POST** operation creates a new registration and returns a registration identifier + - **GET** operation reads existing registrations from the brand registration service + - `/registrations/{registrationId}` : + - **PUT** operation updates an existing registration identified by the registrationId in the brand registration service + - **GET** operation reads an existing registration identified by the registrationId from the brand registration service + - **DEL** operation deletes an existing registration identified by the registrationId from the brand registration service + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + version: wip + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/VerifiedCaller +servers: + - url: '{apiRoot}/brand-registration/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Create Brand registration + description: Create Brand Registration Information for a Calling Party + - name: Update Brand registration + description: Update Existing Brand Registration Information for a Calling Party + - name: Read Brand registration + description: Read Existing Brand Registration Information for a Calling Party + - name: Delete Brand registration + description: Delete Existing Brand Registration Information for a Calling Party +paths: + /registrations: + post: + tags: + - Create Brand registration + summary: Register new brand information in the service platform + description: Register new brand information with optional call verification request. + operationId: createRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateOrUpdateRegistrationRequest' + examples: + INPUT_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Create a registration for a device, identified by a phone number + value: + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + INPUT_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: Create a registration for a device, identified by a phone number & phone number alternate + value: + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + + responses: + '201': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Create404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/CreateOrUpdateRegistrationUnprocessableEntity422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:create + get: + tags: + - Read Brand registration + summary: Read existing brand registrations from the service platform + description: Read existing brand registrations from the service platform. + operationId: readRegistrations + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/Page' + - $ref: '#/components/parameters/PerPage' + - $ref: '#/components/parameters/Seek' + responses: + '200': + $ref: '#/components/responses/SuccessfulRecords' + '204': + $ref: '#/components/responses/204NoContent' + '206': + $ref: '#/components/responses/SuccessfulPartialRecords' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:read + + /registrations/{registrationId}: + get: + tags: + - Read Brand registration + summary: Read an existing brand registration from the service platform + description: Read an existing brand registration from the service platform + operationId: readRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + responses: + '200': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:read + delete: + tags: + - Delete Brand registration + summary: Delete an existing brand registration from the service platform + description: Delete an existing brand registration from the service platform + operationId: deleteRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + responses: + '204': + $ref: '#/components/responses/204NoContent' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:delete + put: + tags: + - Update Brand registration + summary: Update an existing brand registration in the service platform + description: Update an existing brand registration + operationId: updateRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + - description: Unique identifier of an existing brand registration + in: path + name: registrationId + required: true + schema: + type: string + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreateOrUpdateRegistrationRequest' + examples: + INPUT_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Update registration for a device, identified by a phone number + value: + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + INPUT_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: Update registration for a device, identified by a phone number & phone number alternate + value: + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + + responses: + '200': + $ref: '#/components/responses/SuccessfulRecord' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Update404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/CreateOrUpdateRegistrationUnprocessableEntity422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - brand-registration:update + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Page: + name: page + in: query + description: | + Indicates the subset of entries to be returned, where total number of pages is determined by the number of all applicable entries and the value of the *perPage* parameter. + *First page is indicated with value 0.* + schema: + type: integer + default: 0 + PerPage: + name: perPage + in: query + description: Indicates the number of entries to be returned in each response. Has no effect if total number of applicable entries < perPage. + schema: + type: integer + default: 10 + Seek: + name: seek + in: query + description: Indicates the last entry read, to create the next/previous subset of entries in the response of the current query. + schema: + type: string + + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + Content-Last-Key: + description: Indicates the index of the last entry provided in the response + schema: + type: string + X-Total-Count: + description: Total number of applicable entries + schema: + type: integer + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + RegistrationId: + type: string + format: uuid + description: Unique identifier of a registration created in the Branded Calling Platform as a result of the POST operation. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + CustomerId: + type: string + description: Unique customer identifier for a brand + example: "Customer1" + + DisplayName: + type: string + maxLength: 32 + description: Brand information that will be displayed for the calling party + example: "Company X Call Center" + + DisplayAsset: + type: string + format: uri + description: > + Resource URI for a visual asset (e.g. a logo, image or video) that is to be displayed to the called party. + The URI MAY be in IMS-style and include semicolon-separated URI parameters in accordance + with SIP / RFC 3261 conventions (e.g. ';purpose=icon'). + This URI is a logical identifier inside the service provider's network and is not guaranteed to be + resolvable by general-purpose HTTP clients. + Support of the DisplayAsset depends on the service provider and called party's device. + example: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + + VerifyCallerAction: + type: string + description: >- + Indicates if Antispoofing feature is enabled for the A-party, if enabled what action to take in case antispoofing check fails. Absence of parameter means feature not enabled. + example: "DO_NOT_BRAND" + enum: + - "BLOCK_UNVERIFIED" + - "DO_NOT_BRAND" + + TerminatingCountryCode: + type: integer + description: Country Code of the called number in E.164 format + example: 44 + + CampaignName: + type: string + description: Logical name to group a set of calling party numbers under a brand for a specific purpose, e.g. special charging + example: "Company X New Year Sales" + + CreateOrUpdateRegistrationRequest: + type: object + description: "Request object to create or update (replace) a brand registration" + required: + - "phoneNumber" + - "displayName" + - "terminatingCountryCode" + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + phoneNumberAlternate: + $ref: '#/components/schemas/PhoneNumber' + displayName: + $ref: '#/components/schemas/DisplayName' + displayAsset: + $ref: '#/components/schemas/DisplayAsset' + customerId: + $ref: '#/components/schemas/CustomerId' + verifyCallerAction: + $ref: '#/components/schemas/VerifyCallerAction' + terminatingCountryCode: + $ref: '#/components/schemas/TerminatingCountryCode' + campaignName: + $ref: '#/components/schemas/CampaignName' + + RegistrationRecord: + type: object + description: "Object to represent a single brand registration in the service platform" + required: + - "registrationId" + - "phoneNumber" + - "displayName" + - "terminatingCountryCode" + properties: + registrationId: + $ref: '#/components/schemas/RegistrationId' + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + phoneNumberAlternate: + $ref: '#/components/schemas/PhoneNumber' + displayName: + $ref: '#/components/schemas/DisplayName' + displayAsset: + $ref: '#/components/schemas/DisplayAsset' + customerId: + $ref: '#/components/schemas/CustomerId' + verifyCallerAction: + $ref: '#/components/schemas/VerifyCallerAction' + terminatingCountryCode: + $ref: '#/components/schemas/TerminatingCountryCode' + campaignName: + $ref: '#/components/schemas/CampaignName' + + RegistrationRecords: + type: array + items: + $ref: '#/components/schemas/RegistrationRecord' + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + SuccessfulRecord: + description: Success response with a brand registration record + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecord' + examples: + RECORD_SINGLE_PHONE_NUMBER: + summary: Device identified by phoneNumber + description: Registration for a device, identified by a phone number + value: + registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + RECORD_TWO_PHONE_NUMBERS: + summary: Device identified by phoneNumber & phoneNumberAlternate + description: A registration for a device, identified by both a phone number and a phone number alternate + value: + registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + phoneNumberAlternate: "+123456790" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "DO_NOT_BRAND" + SuccessfulRecords: + description: Success response with one or more brand registration records + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecords' + examples: + TWO_RECORDS_FOUND: + summary: Two registration records available + description: Two registration records returned to the client + value: + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794833" + phoneNumber: "+123456790" + phoneNumberAlternate: "+123456791" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + customerId: "Customer2" + verifyCallerAction: "BLOCK_UNVERIFIED" + 204NoContent: + description: Successful response with no content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + SuccessfulPartialRecords: + description: | + Success response with one or more brand registration records. + Used if the request expects a paginated response. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + Content-Last-Key: + $ref: "#/components/headers/Content-Last-Key" + X-Total-Count: + $ref: "#/components/headers/X-Total-Count" + content: + application/json: + schema: + $ref: '#/components/schemas/RegistrationRecords' + examples: + TWO_RECORDS_FOUND: + summary: Two registration records available + description: Two registration records returned to the client + value: + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794832" + phoneNumber: "+123456789" + terminatingCountryCode: 44 + displayName: "Company X Calling" + customerId: "Customer1" + verifyCallerAction: "DO_NOT_BRAND" + - registrationId: "ea77c42f-fa5e-4612-cb43-d502ae794833" + phoneNumber: "+123456790" + phoneNumberAlternate: "+123456791" + terminatingCountryCode: 44 + displayName: "Company Y Calling" + displayAsset: "https://ims.operator-name.com/brand-logo.bmp;purpose=icon" + customerId: "Customer2" + verifyCallerAction: "BLOCK_UNVERIFIED" + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + summary: Unauthenticated + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Create404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + DEVICE_NOT_FOUND: + summary: Device not found + description: The device is not known to the service provider + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: 'The device is not known to the service provider' + Update404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + BRAND_REGISTRATION_404_REGISTRATION_NOT_FOUND: + summary: Registration not found + description: The brand registration service is not able to identify the registration + value: + status: 404 + code: BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + message: 'The brand registration service is not able to identify an existing registration' + DEVICE_NOT_FOUND: + summary: Device not found + description: The device is not known to the service provider + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: 'The device is not known to the service provider' + Generic404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + BRAND_REGISTRATION_404_REGISTRATION_NOT_FOUND: + summary: Registration not found + description: The brand registration service is not able to identify the registration + value: + status: 404 + code: BRAND_REGISTRATION.REGISTRATION_NOT_FOUND + message: 'The brand registration service is not able to identify an existing registration' + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + summary: Conflict + description: Requested operation conflicts with existing data in the service platform + value: + status: 409 + code: CONFLICT + message: Requested operation conflicts with existing data in the service platform + CreateOrUpdateRegistrationUnprocessableEntity422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + summary: Generic Internal + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: "Internal server error" + Generic503: + description: Service unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + summary: Generic Unavailable + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" diff --git a/original/VerifiedCaller/code/API_definitions/verified-caller.yaml b/original/VerifiedCaller/code/API_definitions/verified-caller.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f319c3c95e947bd1e83071c692c0a2816346e7b5 --- /dev/null +++ b/original/VerifiedCaller/code/API_definitions/verified-caller.yaml @@ -0,0 +1,496 @@ +openapi: 3.0.3 +info: + title: Verified Caller + description: | + This API provides the ability to verify the authenticity of a call from a calling party to a specific called party. + + # Introduction + + Consumers of Verified Caller API can initiate the verification of the authenticity of a call from a calling party to a specific called party. A relationship between the API consumer and the service provider has to be already established for a calling party. This can be achieved by using the brand-registration API, or another mechanism agreed upon by the API consumer and the service provider. + + Verified Caller API could be useful in scenarios such as: + - Telesales + - Customer Support + - Outreach efforts of NGOs. + - Calls placed by authorities or government institutions for official matters. + + # Relevant terms and definitions + + * **callingParticipant** and **calledParticipant**: A pair of E.164 numbers representing the parties in a call. + * **registrationId** : A unique reference to the relationship between the API consumer and the service provider. + * **strategy**: Indicator of the requested method to be applied by the service provider to verify a call, as desired by the API consumer. + * **timeToLive**: The period for which the verification by the service provider remains valid. A call is not considered as verified if it is placed after expiry of verification. The service provider may choose to reject a request based on the requested timeToLive value, or apply a different value than requested by the API consumer. The service provider shall observe a timeToLive value for all accepted requests. In order to reduce the risk of a spoofed call, the service provider is advised to expire the verification right away once the call is placed. + * **dynamicDisplayName**: If strategy is 'BRAND_DISPLAY' and this parameter is provided, it overrides any pre-arranged display name presented to the callee, e.g. one set using the brand-registration API request. + + # API Functionality + The API exposes the following endpoints/operations: + - `/pre-announce` : + - **POST** operation creates a new pre-announcement for a call + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Identifying the device from the access token + + Not applicable as this API requires the API consumer to identify the called party as the subject of the API using the mandatory `calledParticipant` object. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + + # Further info and support + + (FAQs will be added in a later version of the documentation) + + version: wip + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + x-camara-commonalities: 0.6 +externalDocs: + description: Project documentation at Camara + url: https://github.com/camaraproject/VerifiedCaller +servers: + - url: '{apiRoot}/verified-caller/vwip' + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Create Pre-announcement + description: Create a call pre-announcement for a Calling and a Called Party +paths: + /pre-announce: + post: + tags: + - Create Pre-announcement + summary: Create a call pre-announcement in the service platform + description: Create a call pre-announcement for a Calling and a Called Party that will remain valid for a specified duration. + operationId: createPreAnnouncement + parameters: + - $ref: '#/components/parameters/x-correlator' + requestBody: + required: true + content: + application/json: + schema: + $ref: '#/components/schemas/CreatePreAnnouncementRequest' + examples: + USING_SMS: + summary: A short message is sent to the callee to verify authenticity of the caller + description: A short message is sent to the callee to verify authenticity of the caller + value: + callingParticipant: "+123456789" + calledParticipant: "+123456792" + strategy: "SMS" + timeToLive: 45 + registrationId: "d011cbff-cf79-4db3-a72b-8164aa894b37" + USING_BRAND_DISPLAY: + summary: A displayName is displayed to the callee to verify authenticity of the caller + description: A displayName is displayed to the callee to verify authenticity of the caller + value: + callingParticipant: "+123456791" + calledParticipant: "+123456792" + strategy: "BRAND_DISPLAY" + timeToLive: 45 + registrationId: "d011cbff-cf79-4db3-a72b-8164aa894b37" + dynamicDisplayName: "Company X Re: Your Complaint" + + responses: + '201': + $ref: '#/components/responses/Create201' + '204': + $ref: '#/components/responses/Create204' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Create404' + '409': + $ref: '#/components/responses/Generic409' + '422': + $ref: '#/components/responses/Create422' + '429': + $ref: '#/components/responses/Generic429' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + + security: + - openId: + - verified-caller:create + +components: + securitySchemes: + openId: + description: OpenID Connect authentication + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + PreAnnouncementId: + type: string + format: uuid + description: Unique identifier of a pre-announcement created as a result of the POST operation. Reserved for future use. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + TimeToLive: + type: integer + minimum: 1 + maximum: 86400 + description: This parameter specifies for how long the pre-announcement is valid, in units of seconds. Calls processed after the call pre-announcement expiry shall be treated as not announced. If not specified, the service provider applies a default value. The service provider may enforce an upper bound of their choosing while validating the request. + example: 60 + + RegistrationId: + type: string + format: uuid + description: Unique identifier of a relatonship created between the API consumer and the service platform. + example: "9e765f76-8037-4e5f-ba5d-e0c87c09a320" + + DynamicDisplayName: + type: string + maxLength: 32 + description: Brand information that will be displayed to the calling party if strategy is 'BRAND_DISPLAY'. If provided, this value overrides a pre-configured display name, e.g. the displayName parameter provided in the brand-registration API request. + example: "Company X Call Center" + + Strategy: + type: string + description: The method to be applied to verify the authenticity of the calling party. Absence of this parameter lets the service provider choose a default strategy which the API consumer must beware. + enum: + - "SMS" + - "BRAND_DISPLAY" + + CreatePreAnnouncementRequest: + type: object + description: "Request object to create a call pre-announcement" + required: + - "callingParticipant" + - "calledParticipant" + properties: + callingParticipant: + $ref: '#/components/schemas/PhoneNumber' + calledParticipant: + $ref: '#/components/schemas/PhoneNumber' + strategy: + $ref: '#/components/schemas/Strategy' + timeToLive: + $ref: '#/components/schemas/TimeToLive' + registrationId: + $ref: '#/components/schemas/RegistrationId' + dynamicDisplayName: + $ref: '#/components/schemas/DynamicDisplayName' + + ExpiresAt: + type: string + format: date-time + description: | + Date when the validity of call verification will expire. The call must be placed up to this date for the service provider to verfiy it. The service provider may inlcude it especially if the API consumer did not specify a timeToLive in the request, or the service provider chose to apply a different value than requested. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + Recommended format is yyyy-MM-dd'T'HH:mm:ss.SSSZ (i.e. which allows 2023-07-03T14:27:08.312+02:00 or 2023-07-03T12:27:08.312Z) + example: "2023-07-03T12:27:08.312Z" + + AnnouncementInfo: + type: object + description: "Object to represent the creation of a single pre-announcement in the service platform" + properties: + preAnnouncementId: + $ref: '#/components/schemas/PreAnnouncementId' + expiresAt: + $ref: '#/components/schemas/ExpiresAt' + + ErrorInfo: + description: Common schema for errors + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP status code returned along with this error response + code: + type: string + description: Code given to this error + message: + type: string + description: Detailed error description + + responses: + Create201: + description: Successful creation of a pre-announcement + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/AnnouncementInfo' + examples: + SUCCESSFUL_CREATION: + summary: Success response with optional parameters + description: Successful pre-announcement of a call. The service platform includes optional parameter(s) to inform the client. + value: + preAnnouncementId: "be5105dc-9b0e-437b-a03e-6e6ffb5e50c0" + expiresAt: "2023-07-03T12:27:08.312Z" + + Create204: + description: Successful creation of a pre-announcement with no content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + summary: Invalid argument + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + summary: Unauthenticated + description: Request cannot be authenticated + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + summary: Permission denied + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + Create404: + description: Not found + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - GENERIC_404_IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + summary: Generic Not Found + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: "{{resource}} is not found" + DEVICE_NOT_FOUND: + summary: Device not found + description: Device is not found + value: + status: 404 + code: GENERIC_404_IDENTIFIER_NOT_FOUND + message: "Call Participant {{number}} is not known to the service provider" + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - CONFLICT + examples: + GENERIC_409_CONFLICT: + summary: Conflict + description: Requested operation conflicts with existing data in the service platform. That may point to a mismatch between the request and existing relationship between the API consumer and the service provider. + value: + status: 409 + code: CONFLICT + message: Requested operation conflicts with existing data in the service platform + Create422: + description: Unprocessable Content + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + summary: Service not applicable + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Either out of resource quota or reaching rate limiting. + GENERIC_429_TOO_MANY_REQUESTS: + description: API Server request limit is overpassed + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Either out of resource quota or reaching rate limiting. + Generic500: + description: Internal server error + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_500_INTERNAL: + summary: Generic Internal + description: Problem in Server side. Regular Server Exception + value: + status: 500 + code: INTERNAL + message: "Internal server error" + Generic503: + description: Service unavailable + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/ErrorInfo" + examples: + GENERIC_503_UNAVAILABLE: + summary: Generic Unavailable + description: Service is not available. Temporary situation usually related to maintenance process in the server side + value: + status: 503 + code: UNAVAILABLE + message: "Service unavailable" diff --git a/original/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story.md b/original/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story.md new file mode 100644 index 0000000000000000000000000000000000000000..71ceeed2f6978adab67f8275cd586aac1b322cf8 --- /dev/null +++ b/original/VerifiedCaller/documentation/API_documentation/VerifiedCaller_User_Story.md @@ -0,0 +1,24 @@ + +**User Story: Verified Caller - Registration** +
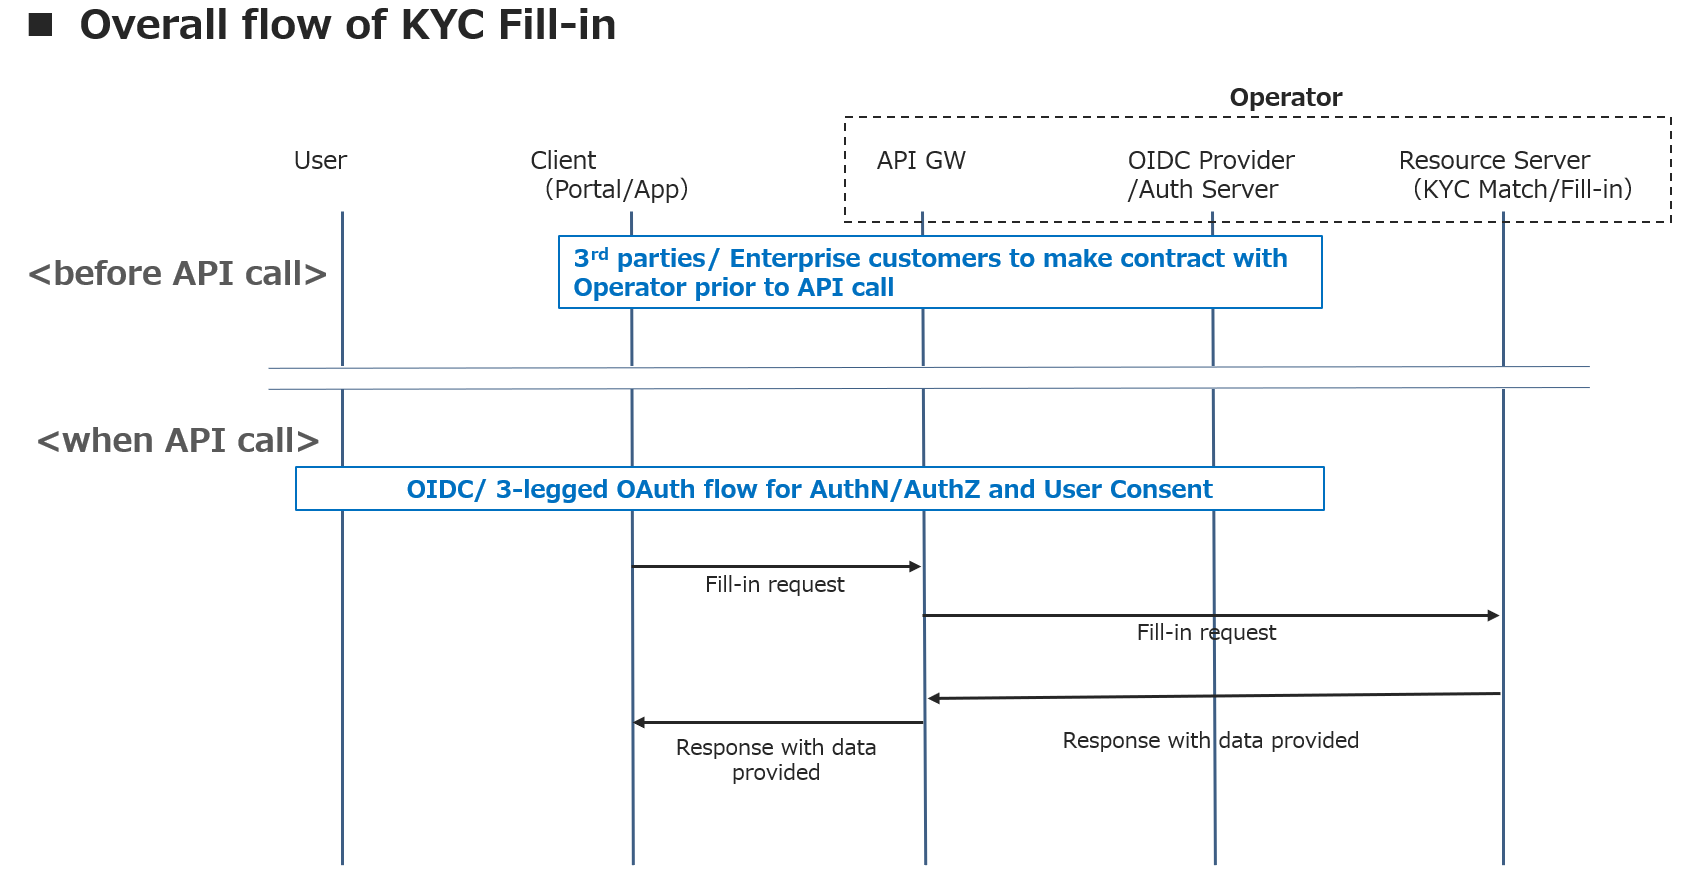
                                                                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to register the display name to be announced for specified caller phone number in the Calling ID solution that I want to use. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                                **Actors:** Mobile Network Operators (MNO), Onboarding/Vetting authority, application developers, enterprise.
                                                                                **Scope:** | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                                1. The Customer:User has provided mandatory information of their identity
                                                                                2. Application developer has onboarded to MNO API
                                                                                3. Application developer has API credentials
                                                                                | +| ***Activities/Steps*** | **Starts when:** The aggregator collect information (display names, phone numbers) and makes a request to the Verified Caller service (API) to register the caller information.
                                                                                **Ends when:** The MNO service returns an register id or an error.
                                                                                | +| ***Post-conditions*** | Branded information are verified and can be approved or rejected. The application developer can make decision to use this customer data to follow-up enterprise processes.| +| ***Exceptions*** | Several exceptions might occur during the Verified Caller API operations:
                                                                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                                • Phone number already used by another customer
                                                                                • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                                                | + +**User Story: Verified Caller - Pre-authorization (i.e. Pre-announcement)** +
                                                                                + +| **Item** | **Details** | +| ---- | ------- | +| ***Summary*** | As an application developer belonging to an enterprise, I want to make my call verified and make the calling id solution displaying a branded announcement previously registered. | +| ***Roles, Actors and Scope*** | **Roles:** Customer:User
                                                                                **Actors:** Mobile Network Operators (MNO), Onboarding/Vetting authority, application developers, enterprise.
                                                                                **Scope:** | +| ***Pre-conditions*** |The preconditions are listed below:
                                                                                1. The Customer:User has provided mandatory information of their identity
                                                                                2. Application developer has onboarded to MNO API
                                                                                3. Application developer has API credentials
                                                                                | +| ***Activities/Steps*** | **Starts when:** The enterprise wants its branded company name be displayed when calling a phone number to avoid any spoofing .
                                                                                **Ends when:** The MNO service returns an acknowledgment or an error.
                                                                                | +| ***Post-conditions*** | The application developer can make decision to use this customer data to follow-up enterprise processes| +| ***Exceptions*** | Several exceptions might occur during the Verified Caller API operations:
                                                                                • Unauthorized: Not valid credentials (e.g. use of already expired access token).
                                                                                • Not Found: The called or caller phone number provided is not managed by the MNO
                                                                                • Invalid input: Not all mandatory input data to invoke operation (e.g. phone number).
                                                                                | diff --git a/original/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist.md b/original/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..dd0d08c29b53e5222bbe7e1160e902d4239111e8 --- /dev/null +++ b/original/VerifiedCaller/documentation/API_documentation/brand-registration-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Brand Registration v0.1.0 in r1.3. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [brand-registration.yaml](/code/API_definitions/brand-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [VerifiedCaller_User_Story.md](/documentation/API_documentation/VerifiedCaller_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/WwPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist.md b/original/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..dc9d57261c8811e9142eb3bc8a4d645117fe52d5 --- /dev/null +++ b/original/VerifiedCaller/documentation/API_documentation/verified-caller-API-Readiness-Checklist.md @@ -0,0 +1,29 @@ +# API Readiness Checklist + +Checklist for Verified Caller v0.1.0 in r1.3. + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----------------:|:-------:|:------:|:----:|:-----------------------------------------------------------------------------------------------------------------:| +| 1 | API definition | M | M | M | M | Y | [verifiedcaller-preannounce.yaml](/code/API_definitions/verifiedcaller-preannounce.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/Commonalities/releases/tag/r3.3) | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | [r3.3](https://github.com/camaraproject/IdentityAndConsentManagement/releases/tag/r3.3) | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | Y | [VerifiedCaller_User_Story.md](/documentation/API_documentation/VerifiedCaller_User_Story.md) | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [/code/Test_definitions](/code/Test_definitions) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | r1.3 | +| 11 | Change log updated | M | M | M | M | Y | [CHANGELOG.md](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/x/WwPWB) | + +To fill the checklist: +- in the line above the table, replace the api-name, api-version and the rx.y by their actual values for the current API version and release. +- in the Status column, put "Y" (yes) if the release asset is available or fulfilled in the current release, a "N" (no) or a "tbd". Example use of "tbd" is in case an alpha or release-candidate API version does not yet provide all mandatory assets for the release. +- in the Reference information column, provide the relative links (from the API repository home folder) to the release asset once available, the applicable release numbers (not versions) of Commonalities and ICM, and any other relevant links or information. +- For the point 12: The Reference information comment shall reference a note (e.g. "see (1)") under the checklist table to be added that states the certified company(s) as can be found on the following link: [GSMA Open Gateway Portal](https://open-gateway.gsma.com/). + +Note: the checklists of a public API version and of its preceding release-candidate API version can be the same. + +The documentation for the content of the checklist is here: see API Readiness Checklist section in the [API Release Process](https://lf-camaraproject.atlassian.net/wiki/x/jine). diff --git a/original/VoiceNotification/README.md b/original/VoiceNotification/README.md new file mode 100644 index 0000000000000000000000000000000000000000..46384910a9fd1add554346f82733b3ea5e0c1081 --- /dev/null +++ b/original/VoiceNotification/README.md @@ -0,0 +1,43 @@ + + + + + + + + + +# VoiceNotification + +Sandbox API Repository to describe, develop, document, and test the VoiceNotification Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/owAbBw) + +## Scope + +* Service API(s) “VoiceNotification” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: May 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/owAbBw) !! update this link to your minutes archive page using the "Share" link and delete the task +* Mailing List + + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/VoiceNotification/code/API_definitions/README.MD b/original/VoiceNotification/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/VoiceNotification/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/VoiceNotification/documentation/API_documentation/README.MD b/original/VoiceNotification/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/VoiceNotification/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/VoiceNotification/documentation/SupportingDocuments/README.MD b/original/VoiceNotification/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/VoiceNotification/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/VoiceVerificationCode/README.md b/original/VoiceVerificationCode/README.md new file mode 100644 index 0000000000000000000000000000000000000000..6c7bb876115cce5670e1974c42e4016e404f23b4 --- /dev/null +++ b/original/VoiceVerificationCode/README.md @@ -0,0 +1,42 @@ + + + + + + + + + +# VoiceVerificationCode + +Sandbox API Repository to describe, develop, document, and test the VoiceVerificationCode Service API(s) within the Sub Project [Number Insights](https://lf-camaraproject.atlassian.net/wiki/x/BYEpBQ). + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/nID7Bw) + +## Scope + +* Service API(s) “VoiceVerificationCode” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * §Short API scope description§ !! ⚠️ Add here a scope description according to the API proposal +* Describe, develop, document, and test the API(s) +* Started: June 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + +## Contributing + +* Meetings are held virtually + + * Schedule: !! tbd + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meetings/telcoapi) !! Update this link with your meeting registration/join link and delete the task + * Minutes: Access [meeting minutes](https://lf-camaraproject.atlassian.net/wiki/x/nID7Bw) !! update this link to your minutes archive page using the "Share" link and delete the task +* Mailing List + * Subscribe / Unsubscribe to the mailing list . + * A message to the community of this Sub Project can be sent using . diff --git a/original/VoiceVerificationCode/code/API_definitions/README.MD b/original/VoiceVerificationCode/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/VoiceVerificationCode/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/VoiceVerificationCode/documentation/API_documentation/README.MD b/original/VoiceVerificationCode/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/VoiceVerificationCode/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/VoiceVerificationCode/documentation/SupportingDocuments/README.MD b/original/VoiceVerificationCode/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/VoiceVerificationCode/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/WebRTC/README.md b/original/WebRTC/README.md new file mode 100644 index 0000000000000000000000000000000000000000..36f677b2d748650c807a57aaf5d661b32d98356a --- /dev/null +++ b/original/WebRTC/README.md @@ -0,0 +1,71 @@ + + + + + + + + + +# WebRTC + +Sandbox API Repository to describe, develop, document, and test the WebRTC Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/MS7e) + +## Scope +* Service APIs for “WebRTC” (see APIBacklog.md) +* It provides the API consumer with the ability to: + * Add real-time communication capabilities to their applications like video, voice, and generic data. + * Enable an API consumer to register for communication services through a network using Oauth 2.0 and OIDC. + * Create subscriptions to receive call notifications using CloudEvents: Ability to follow the call establishment process and to receive new incoming calls. + * Make and receive calls from the API consumer (client) side establishing a realiable media session to securely exchange media. +* Describe, develop, document and test the APIs (with 1-2 Telcos) +* Started: September 2023 + + + + +## Release Information + +> [!NOTE] +> Please be aware that the project will have frequent updates to the main branch. There are no compatibility guarantees associated with code in any branch, including main, until a new release is created. For example, changes may be reverted before a release is created. **For best results, use the latest available release**. + +* **NEW**: The latest public release is [r2.2](https://github.com/camaraproject/WebRTC/releases/tag/r2.2) (Fall25), with the following API versions: + * **webrtc-call-handling v0.3.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-call-handling.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-call-handling.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-call-handling.yaml) + * **webrtc-events v0.2.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-events.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-events.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-events.yaml) + * **webrtc-registration v0.3.0** + [[YAML]](https://github.com/camaraproject/WebRTC/blob/r2.2/code/API_definitions/webrtc-registration.yaml) + [[ReDoc]](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-registration.yaml&nocors) + [[Swagger]](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/r2.2/code/API_definitions/webrtc-registration.yaml) +* The latest public release is always available here: https://github.com/camaraproject/WebRTC/releases/latest +* Other releases of this repository are available in https://github.com/camaraproject/WebRTC/releases +* For changes see [CHANGELOG.md](https://github.com/camaraproject/WebRTC/blob/main/CHANGELOG.md) + +_The above section is automatically synchronized by CAMARA project-administration._ + + +## API Extra documentation + +* Find API reference documentation at folder: [code/API_definitions](code/API_definitions/) +* Find API testing documentation at folder: [code/Test_definitions](code/Test_definitions/) +* Find release status documentation at folder: [documentation/API_documentation](documentation/API_documentation) +* Find UML and complementary documentation at folder: [documentation/SupportingDocuments](documentation/SupportingDocuments) +* For other information refer to [Confluence CAMARA project wiki](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14560817/WebRTC) + +## Meetings +* Meetings are held virtually + * Find meeting notes at https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564608/Minutes+-+WebRTC +* Schedule: + * Tuesdays 4pm CEST (Madrid, Paris, Berlin, Rome), each 15 days + +## Contributorship and mailing list + +* To subscribe / unsubscribe to the mailing list of this Sub Project and thus be / resign as Contributor please visit . +* A message to all Contributors of this Sub Project can be sent using . diff --git a/original/WebRTC/code/API_definitions/README.MD b/original/WebRTC/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..5816bf31722b78544ae188def79fc0eeacad7fc1 --- /dev/null +++ b/original/WebRTC/code/API_definitions/README.MD @@ -0,0 +1,47 @@ +# WebRTC APIs definitions + +This folder contain the OpenAPI definitions of the WebRTC subgroup + +## APIs included + +* `webrtc-registration` [Registration and Authentication management](webrtc-registration.yaml) + * This API definition provides functionality for a REST client, browser or native application to manage Registration and Connectivity (RACM) towards Internet Multimedia Subsystem (IMS) Network. + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-registration.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-registration.yaml) + +* `webrtc-call-handling` [Call handling service](webrtc-call-handling.yaml) + * This API definition provides functionality for REST clients, browser or native application, to create and manage 1-1 calling. Both incoming and outgoing. + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-call-handling.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-call-handling.yaml) + +* `webrtc-events` [WebRTC Event Subscription](webrtc-events.yaml) + * This API definition provides functionality for REST clients, browser or native application, to track session events. This will allow the client to receive server side updates about new incoming calls and other needed updates regarding the media negotiation and session progress (ringing, hangup, etc). + * [View main on ReDoc](https://redocly.github.io/redoc/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-events.yaml&nocors) + * [View main on Swagger Editor](https://camaraproject.github.io/swagger-ui/?url=https://raw.githubusercontent.com/camaraproject/WebRTC/main/code/API_definitions/webrtc-events.yaml) + +Detailed descriptions, diagrams and more information could be found at [API documentation](../../documentation/API_documentation/) section + +## Check APIs online + +Use the previous links to check the DEV main version of the API. Copy & paste any raw file to check them: + +* ReDoc: https://redocly.github.io/redoc/ +* Swagger: https://editor.swagger.io/ +* CAMARA dedicated swagger instance: https://camaraproject.github.io/swagger-ui/ + + +## Build HTML from sources + +Build an HTML from sources using a local build OpenAPI v3 compatible like Node `redocly/cli` + +Execute redocly for each API document, use -o to +``` +$ npx @redocly/cli build-docs API_description_file.yaml +``` + +Or install the tool globaly and then build it +``` +$ npm install @redocly/cli -g + +$ redocly build-docs API_description_file.yaml +``` \ No newline at end of file diff --git a/original/WebRTC/code/API_definitions/webrtc-call-handling.yaml b/original/WebRTC/code/API_definitions/webrtc-call-handling.yaml new file mode 100644 index 0000000000000000000000000000000000000000..41dbac78ade18e0d8ecadc5a5fe7cdff76481043 --- /dev/null +++ b/original/WebRTC/code/API_definitions/webrtc-call-handling.yaml @@ -0,0 +1,918 @@ +openapi: 3.0.3 +info: + title: WebRTC Call Handling + description: |- + # Introduction + + This API provides REST API for clients to manage live audio and video sessions + towards the operator's network (IMS network). + + To handle audio/video sessions, what we usually known as *calls*, the network + requires to identify both involved parties: caller, the origin, and the callee, + the destination. Once the involved communication endpoints are identified, + the endpoints need to negotiate *how* to send media from one endpoint to the other. + + The first step, *identify the endpoints* is handled through + parameters in the API request. The latter step, *negotiate how to connect*, is done by + sharing media transmission requirements (called SDP information) between the involved endpoints. + + In this step, the WebRTC technology is used to simplify the access to the + media, and get a simple and well-known protocol to negotiate the media transmission + requirements. + + Let's dig into more details on section 3: API functionality + + **Use cases to cover:** + - Functional: + - Ability to create audio and video sessions on the network, this grants + ability to reach any phone number on the public network using your telco + provider rights. + - Ability to retrieve any session, to recover for a network disconnection + or to check current status for any reason. + - Ability to upgrade to video, change sending audio/video parameters, or + notify the network about any modification on your side of the calls. + - Ability to hangup the call. Stop the transmission, and delete your audio + and video session. + - An additional subscription to webrtc-events API is required to receive + incoming events from network side (ex. remote hangup event). + + # Relevant terms and definitions + + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a **media session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **deviceId**: A unique identifier for the physical device where a media + session is initiated. It is provided by the WebRTC application, it remains + consistent across multiple installations or logins on the same device. Its + primary function is to ensure that only one WebRTC session (**registration**) + is active per device at a time, enabling the network to clean up any stale + sessions if a new session is initiated on the same device. + - **registration**: A device status in which the device is properly + identified and recognized as reachable by the server side of the network. + - **registrationId**: Unique identifier of an device **registration**. + Retrieved using the `webrtc-registration` API + - **x-correlator**: Unique ID included in the API request created by the API consumer. + It is used to correlate an API request with its response and help in debugging. + - **WebRTC**: WebRTC is a free and open-source project providing web browsers + and mobile applications with real-time communication via application programming + interfaces. It allows audio and video communication and streaming to work + inside web pages by allowing direct peer-to-peer communication + - **SDP**: Acronym for Session Description Protocol. The SDP is a format for + describing multimedia communication sessions for the purposes of announcement + and invitation. + - **WrtcSDPDescriptor**: Schema to include inside a JSON, a SDP body. You can + obtain an SDP for WebRTC calling using the WebRTC API provided by the browser + or any other media library. + + # API functionality + + This API allows to create 1-1 voice and video sessions. These, identified by a + unique `mediaSessionId` can be recovered, updated and terminated via this API + and its methods. + - **POST**: Create a new session using a valid `registrationId` from registration API + - **GET**: Recover an existing session via its unique `mediaSessionId` + - **DELETE**: Finish an existing session via its unique `mediaSessionId` + - **PUT**: Update the status of a session via its unique `mediaSessionId` + + To receive updates from the network about the session establishment process, you + must use `webrtc-events` API. + + ## 1. Creating a call + + To call someone, you need, previously a valid registration on the network. + You must check the webrtc-registration API to retrieve a valid registration + on the network that allows you to send calls (IMS registration). + + Once this is completed, you can consume the POST /sessions/ endpoint to call + a remote destination. + + ``` + POST /webrtc-call-handling/v0.2/sessions + { + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + } + ``` + + This will create a call, but without local media you will have a problem, or + maybe the network will reject your call. You need to add a local SDP offer. + + > **The WebRTC SDP local candidate** + > + > What is usually done, before attempt to create a call, is to solve the SDP local + description. This is, how you are going to send the media. To explain it briefly, + browsers offer the + [WebRTC API](https://developer.mozilla.org/en-US/docs/Web/API/WebRTC_API) that + include `getUserMedia()` and `RTCPeerConnection` interfaces that will simplify + the process. + > + > In summary, we need to obtain the media, create the `RTCPeerConnection` + and use it's SDP on our CAMARA webrtc-call-handling API as the offer. There + is extra information about this concept on the SupportingDocuments folder. + + Once you retrieve you local SDP offer, you modify your session including it, + or maybe you prefer to solve the local candidate before attempt the call, in + that case, you will include your local offer on the audio/video session creation. + + ``` + POST /webrtc-call-handling/v0.2/sessions + { + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + "offer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + } + } + ``` + + Following this point, your call is progressing and the network will inform + about extra information required and connection status via de the + webrtc-events API. + + Check webrtc-events API inline documentation and supporting documents + for further information. + + ## 2. Hanging up a call + + When you have a voice/video session in progress, you can decide to finish the + call, to do so, simply execute a DELETE request of the session using the + `mediaSessionId` obtained on call creation. + + This action will trigger all necessary action on the network side to properly + hangup and drop the call. + + ## 3. Picking up a call + + Using the `webrtc-events` API, you can receive events from the network, these + events could include the `session-invitation` event. This means that someone + is calling you. + + To *hook off*, we need to retrieve the session based on the `mediaSessionId` + using the GET request, afterwards, you can present to the user some + confirmation option to accept the call. + + Final step is to include a local offer. We already seen at 3.1 that a local + SDP is required, in this case, we will use the PUT request to modify the + audio/video session and include the information about the responding device. + + Let's say that we are responding this session `0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD`: + ``` + PUT /webrtc-call-handling/v0.2/sessions/0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD/status + { + "status": "InProgress", + "answer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + } + } + ``` + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + # Emergency Calling + - Introduces a new `callType` attribute with values `REGULAR` or `EMERGENCY`. + - When `callType` is `EMERGENCY`, the client **MAY** include `locationDetails` + describing the caller's location. + - `locationDetails` follows PIDF-LO concepts (3GPP TS 24.229, RFC 4119, RFC 5139, + RFC 5491) with either a circle or ellipsoid shape. + - If `callType` is omitted, it defaults to `REGULAR`. + + license: + name: Apache 2.0 + url: 'https://www.apache.org/licenses/LICENSE-2.0.html' + version: 0.3.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: '{apiRoot}/webrtc-call-handling/v0.3' + variables: + apiRoot: + description: API root + default: 'http://localhost:9091' +tags: + - name: Call handling + description: Operations to manage voice video sessions (calls) +paths: + /sessions: + post: + tags: + - Call handling + summary: Creates voice and/or video session + description: Creates a voice and/or video session + operationId: createSession + parameters: + - $ref: "#/components/parameters/x-correlator" + - $ref: '#/components/parameters/hdrRegistrationId' + security: + - openId: + - webrtc-call-handling:sessions:create + requestBody: + description: Provide the information required for session creation + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Media session request: + $ref: '#/components/examples/exampleMediaSessionRequest' + EmergencyMediaSessionRequest: + $ref: '#/components/examples/exampleEmergencyMediaSessionRequest' + responses: + '201': + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + SessionCreated: + $ref: '#/components/examples/exampleMediaSessionResponse' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: '#/components/responses/Generic403' + '501': + description: Not Implemented + headers: + x-correlator: + $ref: '#/components/headers/x-correlator' + content: + application/json: + schema: + allOf: + - $ref: '#/components/schemas/ErrorInfo' + - type: object + properties: + status: + enum: + - 501 + code: + enum: + - CALLTYPE_EMERGENCY_NOT_SUPPORTED + examples: + 501_CALLTYPE_EMERGENCY_NOT_SUPPORTED: + description: The implementation of API provider does not support the `callType` of `EMERGENCY`. + value: + status: 501 + code: CALLTYPE_EMERGENCY_NOT_SUPPORTED + message: Server does not support call type EMERGENCY. + /sessions/{mediaSessionId}: + get: + tags: + - Call handling + summary: Get the media session information + description: | + Get the media Session description based on `mediaSessionId`. + + ** The client shall construct the API path using the `mediaSessionId` supplied + in the session creation response (origination) or in the invitation notification + (termination). ** + operationId: getSessionDetailsById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:read + responses: + '200': + description: A session information + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + delete: + tags: + - Call handling + summary: Cancel or Terminate the media session + description: > + Cancel a 1-1 media session (as originator), + + Decline a 1-1 media session (as receiver), + + Terminate a 1-1 an ongoing media session + + ** The client shall construct the API path using the mediaSessionId supplied in the session creation response (origination) or in the invitation notification (termination). **' + operationId: deleteSessionById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:delete + responses: + '204': + description: Session deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + /sessions/{mediaSessionId}/status: + put: + tags: + - Call handling + summary: Update the status of the media session + description: | + Update the status of the media session, this may include updating SDP media + + The API consumer shall construct the API path using the `mediaSessionId` supplied in the session creation response (origination) or in the invitation notification (termination). + operationId: updateSessionStatus + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamMediaSessionId' + security: + - openId: + - webrtc-call-handling:sessions:write + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Update inProgress (update media candidates): + $ref: '#/components/examples/exampleSessionStatus183InProgress' + Update ringing (device user endpoint is ringing): + $ref: '#/components/examples/exampleSessionStatus180Ringing' + Update connected (call is established): + $ref: '#/components/examples/exampleSessionStatus200Connected' + Update hold (call has been placed on call waiting mode): + $ref: '#/components/examples/exampleSessionStatusHold' + Update resume (call has been resumed): + $ref: '#/components/examples/exampleSessionStatusResume' + responses: + '200': + description: | + Updated the session status (with SDP data). + It will confirm the status defined on the PUT operation. + content: + application/json: + schema: + $ref: '#/components/schemas/MediaSessionInformation' + examples: + Update inProgress (update media candidates): + $ref: '#/components/examples/exampleSessionStatus183InProgress' + Update ringing (device user endpoint is ringing): + $ref: '#/components/examples/exampleSessionStatus180Ringing' + Update connected (call is established): + $ref: '#/components/examples/exampleSessionStatus200Connected' + Update hold (call has been placed on call waiting mode): + $ref: '#/components/examples/exampleSessionStatusHold' + Update resume (call has been resumed): + $ref: '#/components/examples/exampleSessionStatusResume' + '204': + description: Updated the session status (no content) + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + hdrRegistrationId: + name: registrationId + in: header + description: The device registration identifier assigned by the network + required: true + style: simple + explode: false + schema: + type: string + pathParamMediaSessionId: + name: mediaSessionId + in: path + description: The sessionId assigned by the network for the media session + required: true + style: simple + explode: false + schema: + type: string + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + MediaSessionInformation: + type: object + properties: + originatorAddress: + $ref: '#/components/schemas/Address' + originatorName: + type: string + description: Friendly name of the call originator + example: 'Alice' + receiverAddress: + $ref: '#/components/schemas/Address' + receiverName: + type: string + description: Friendly name of the call terminator + example: 'Bob' + status: + $ref: '#/components/schemas/SessionStatus' + offer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + answer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + mediaSessionId: + type: string + description: >- + The media session ID created by the network. The mediaSessionId shall not be + included in POST requests by the client, but must be included in the notifications + from the network to the client device. + example: 0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF + callType: + type: string + description: Type of call. When set to EMERGENCY, the client MAY provide locationDetails. If omitted, treated as REGULAR. + enum: + - REGULAR + - EMERGENCY + locationDetails: + $ref: '#/components/schemas/LocationDetails' + WrtcSDPDescriptor: + type: object + description: |- + **OFFER**: An inlined session description in SDP format [RFC4566].If XML syntax + is used, the content of this element SHALL be embedded in a CDATA + section. + + **ANSWER**: This type represents an answer in WebRTC Signaling. This element is not + present in case there is no answer yet, or the session invitation has + been declined by the Terminating Participant.This element MUST NOT be + present in a request from the application to the server to create a + session. + properties: + sdp: + type: string + description: |- + An inlined session description in SDP format [RFC4566].If XML syntax is used, the content of this element SHALL be embedded in a CDATA section + SessionStatus: + type: string + description: Provides the status of the media session. During the session creation, this attribute SHALL NOT be included in the request. + enum: + - Initial + - InProgress + - Ringing + - Proceeding + - Connected + - Terminated + - Hold + - Resume + - SessionCancelled + - Declined + - Failed + - Waiting + - NoAnswer + - NotReachable + - Busy + example: Ringing + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represent + Address: + type: string + description: Subscriber address (Sender or Receiver) + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,}|urn:service:sos(?:\.[a-z0-9](?:[a-z0-9\-]{0,30}[a-z0-9])?)*)$' + example: 'tel:+11234567899' + LocationDetails: + type: object + description: Details about the caller's location and related information. This + object adheres to 3GPP TS 24.229, RFC 4119, RFC 5139, and RFC 5491 for PIDF-LO + compatibility. + properties: + shape: + type: string + enum: + - Circle + - Ellipsoid + description: The shape representing the caller's location (Circle or Ellipsoid). + coordinates: + oneOf: + - $ref: '#/components/schemas/CircleCoordinates' + - $ref: '#/components/schemas/EllipsoidCoordinates' + description: The coordinates of the caller's location, specific to the chosen + shape. + method: + type: string + enum: + - GPS + - DBH + - DBH_HELO + - Other + description: 'The method used to obtain the location information. + + * **GPS:** Global Positioning System (highly accurate) + + * **DBH:** Device-Based Hybrid + + * **DBH_HELO:** Device-Based Hybrid using Apple Hybridized Emergency Location + + * **Other:** Other methods (e.g., landmarks, IP Based etc.) + + ' + confidence: + type: object + description: The confidence level of the location information. + properties: + pdf: + type: string + enum: + - normal + - uniform + description: The probability density function (PDF) associated with the + confidence value. + value: + type: number + minimum: 0 + maximum: 100 + description: The confidence value (percentage). + timestamp: + type: string + format: date-time + description: The timestamp (in ISO 8601 format) indicating when the location + information was Calculated. \nThis is crucial for emergency services to + assess the timeliness of the data. if not provided current timestamp will + be used by default" + CircleCoordinates: + type: object + required: + - latitude + - longitude + - radius + properties: + latitude: + type: number + format: float + description: Latitude of the center point in decimal degrees (WGS84). + longitude: + type: number + format: float + description: Longitude of the center point in decimal degrees (WGS84). + radius: + type: number + format: float + description: Radius of the circle in meters, indicating the uncertainty. + EllipsoidCoordinates: + type: object + required: + - latitude + - longitude + - zAxis + - semiMajorAxis + - semiMinorAxis + - verticalAxis + - orientation + properties: + latitude: + type: number + format: float + description: Latitude in the WGS 84 geocentric coordinate system. + longitude: + type: number + format: float + description: Longitude in the WGS 84 geocentric coordinate system. + zAxis: + type: number + format: float + description: Altitude (optional) in the WGS 84 geocentric coordinate system. + semiMajorAxis: + type: number + description: Length of the semi-major axis of the ellipsoid in meters. + semiMinorAxis: + type: number + description: Length of the semi-minor axis of the ellipsoid in meters. + verticalAxis: + type: number + description: Length of the vertical axis of the ellipsoid in meters. + orientation: + type: number + description: Orientation of the ellipsoid in degrees. + examples: + exampleMediaSessionRequest: + value: + originatorAddress: tel:+17085852753 + originatorName: tel:+17085852753 + receiverAddress: tel:+17085854000 + receiverName: tel:+17085854000 + offer: + sdp: "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:2448:7a05:9b11:66f2:c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:Xm3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\n" + exampleMediaSessionResponse: + value: + originatorAddress: 'tel:+17085852753' + originatorName: 'tel:+17085852753' + receiverAddress: 'tel:+17085854000' + receiverName: 'tel:+17085854000' + offer: + sdp: "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:2448:7a05:9b11:66f2:c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:Xm3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\n" + status: Initial + mediaSessionId: 0AEE1B58BAEEDA3EABA42B32EBB3DFE0DEAD3F90AE0CEB9EEB0C0F703E199FC00E7C6E648F50EE885FF0CE6C7E1CEE795EDD + exampleSessionStatus183InProgress: + value: + receiverSessionStatus: + status: InProgress + answer: + sdp: > + "v=0\r\no=- 8066321617929821805 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 + 0\r\nm= + + audio 42988 RTP/SAVPF 102 113\r\nc=IN IP6 + 2001:e0:410:2448:7a05:9b11:66f2 + + :c9e\r\nb=AS:64\r\na=rtcp:9 IN IP4 + 0.0.0.0\r\na=candidate:1645903805 1 udp + + 2122262783 2001:e0:410:2448:7a05:9b11:66f2:c9e 42988 typhost + generation 0 + + network-id 3 network-cost + 900\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9 + + ggaqxBlHbAFMx\r\na=ice-options:trickle + renomination\r\na=mid:audio\r\na= + + extmap:2 + http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions + + -01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 + AES_CM_128_HMAC_SHA1_80 inline:Xm + + 3YciqVIWFNSwy19e9MvfZ2YOdAZil7oT/tHjdf\r\na=rtpmap:102 + AMR-WB/16000\r\na=fmtp:102 + + octet-align=0; mode-set=0,1,2; + mode-change-capability=2\r\na=rtpmap:113 + telephone-event/16000\r\n" + exampleSessionStatus180Ringing: + value: + receiverSessionStatus: + status: Ringing + exampleSessionStatus200Connected: + value: + receiverSessionStatus: + status: Connected + answer: + sdp: > + "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 + 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN + + IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN + IP4 0.0.0.0\r\na=candidate:3108871805 1 udp + + 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host + generation 0 network-id 3 network-cost 900\r\na= + + ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle + renomination\r\na=mid:audio\r\na= + + extmap:2 + http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r + + \na=crypto:1 AES_CM_128_HMAC_SHA1_80 + inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 + AMR-WAB/16000 + + \r\na=fmtp:102 octet-align=0; mode-set=0,1,2; + mode-change-capability=2\r\na=rtpmap:113 + telephone-event/16000\r\na= + + ptime:20\r\n" + exampleSessionStatusHold: + value: + ReceiverSessionStatus: + status: Hold + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + exampleSessionStatusResume: + value: + ReceiverSessionStatus: + status: Resume + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + exampleEmergencyMediaSessionRequest: + summary: Emergency call initiation with location details + value: + originatorAddress: 'tel:+17085852753' + originatorName: Alice + receiverAddress: 'urn:service:sos' + receiverName: PSAP + offer: + type: offer + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + callType: EMERGENCY + locationDetails: + shape: Circle + coordinates: + latitude: 47.6062 + longitude: -122.3321 + radius: 35 + method: GPS + confidence: + pdf: normal + value: 92 + timestamp: '2025-10-06T19:31:25Z' + responses: + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "originator info is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. diff --git a/original/WebRTC/code/API_definitions/webrtc-events.yaml b/original/WebRTC/code/API_definitions/webrtc-events.yaml new file mode 100644 index 0000000000000000000000000000000000000000..a1f77f7df829924b9cbcc303a0fa4005d449b3d7 --- /dev/null +++ b/original/WebRTC/code/API_definitions/webrtc-events.yaml @@ -0,0 +1,1591 @@ +openapi: 3.0.3 +info: + title: WebRTC Events + description: |- + # Introduction + + This API provide REST API for a client, browser or native application, to + receive events about updates of an active session or new sessions requests + (incoming calls) or registration termination. + + This API allows a WebRTC client to subscribe to events associated with a specific device, + identified by its `deviceId`. The deviceId uniquely represents a physical device on which + registrations and sessions may occur. + + Instead of requiring separate subscriptions per registration (`registrationId`) or per session + (`mediaSessionId`), event delivery is consolidated under the deviceId. This enables the client to + receive all relevant notifications — such as new call invitations or session status updates — + for any registration or session belonging to the same device. + + This allows the device applications to update the UI while media sessions + are progressing and also, allows the device to receive new session request, + generating incoming call scenarios for non-SIM devices. + + A classic use case is the negotiation of a live media session (call), that + requires multiple asynchronous events from server side. Other classic + example, is to notify that a subscriber is not logged into the network + anymore and requires refresh, for example, when the IMS expires the + device registration. + + In addition, this API, allows to an external service to create "notification + channels" for other systems that does no support the async event mechanisms. + For instance, a classic browser using websockets to receive server-side + events. + + **Use cases to cover:** + - Functional: + - A push notification service based on an external webhook + - A browser that requires a WS to receive events from the server side. + - This will require to create a dedicated endpoint using another + network API or external system. + - Observability: + - A monitoring system that wants to monitor registration status of + devices + - A call audit application that requires to remotely monitor call status + + # Relevant terms and definitions + + - **BYON**: Bring Your Own Number. A commercial name for the functionality + to use your network credentials and phone number identity to non-SIM + devices using media sessions. + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a Voice or Video **session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **registration**: A device status in which the device is properly + identified and recognized as reachable by the server side of the network. + - **registrationId**: Unique identifier of an device **registration**. + Retrieved using the `webrtc-registration` API + + # API functionality + + The CAMARA subscription model is detailed in the CAMARA API design guideline + document and follows CloudEvents specification. + + This API allows to create an explicit notification channel for two types of + events. It is mandatory in the subscription to provide the event type for + which the client would like to subscribe. + + Following event types are managed for this API: + + - `org.camaraproject.webrtc-events.v0.session-status` + + - Events triggered for any media session related event (e.g. far end new + media endpoints) + + - `org.camaraproject.webrtc-events.v0.session-invitation` + + - Events triggered when a new session is requested (e.g. incoming call + received) + + - `org.camaraproject.webrtc-events.v0.registration-ends` + + - Events triggered when a webrtc registration is terminated (e.g. webrtc registration expired) + + Note: Additionally to these list, ``org.camaraproject.webrtc-events.v0.subscription-ended`` + notification `type` is sent when the subscription ends. + This notification does not require dedicated subscription. + + It is used when: + - the subscription expire time has been reached (optionally set by the + requester) + - the maximum number of subscription events has been reached (optionally + set by the requester) + - the subscription was deleted by the requester + - the Access Token `sinkCredential` expiration time has been reached + (optionally set by the requester) + - the API server has to stop sending notification prematurely + + ## 1. Session events (session-status) + + Find more information at the Schema description. + + A `org.camaraproject.webrtc-events.v0.session-status` event includes + session information updates. With the same schema that is used with the + WebRTC Call Handling API, when retrieving information from the + `GET /webrtc-call-handling/session/{mediaSessionId}` endpoint. + + In general lines, it is emitted each time that an event happens within the + subscribed session. This might happen when SDP updates are included for any + party or when the call is finished due an ordered cleanup or a service + outage. Any other any relevant internal event could be transmitted through + this channel (eg.: Any SIP response is potentially a + session-status event. + + Regarding the SDP descriptions for offer and answer: + - The offer, which MUST be present in a request from the application to the + server to create a session. Note that the offer can be absent in a session + created by the server as part of an offerless INVITE [RFC3261]. + - For the answer. This type represents an answer in WebRTC Signaling. This + element is not present in case there is no answer yet, or the session + invitation has been declined by the Terminating Participant. This element + MUST NOT be present in a request from the application to the server to + create a session. + + ## 2. New session request (session-invitation) + + Find more information at the Schema description. + + A `org.camaraproject.webrtc-events.v0.session-invitation` event + includes information about new requested sessions (incoming calls), it + requires a valid registration on the network. + + This event is triggered each time that the endpoint is requested to join + an incoming new session. This is done, usually, to indicate that a new + media "call" is incoming. In practical terms, this is a new media + session that requests the endpoint presence. The event include all + functional information required to join the session (media info, caller). + + When a new session is requested, it will include context information: + identification of the caller and other possible carrier data to + contextualize (call subject, branding info, etc). It will also include + a unique SessionId, to create a dedicated subscription and receive events + about the session itself and its status progressing inside the network. + + ## 3. Subscription ends (subscription-ended) + + A `org.camaraproject.webrtc-events.v0.subscription-ended` event indicates that + the endpoint will no longer be notified when a new event occurs. From + the developer's point of view, receiving the subscription-ended event should + signal the need to check the event subscription status and attempt to refresh + it in order to continue receiving new event notifications. + + ## 4. Registration ends (`registration-ends`) + + A `org.camaraproject.webrtc-events.v0.registration-ends` event indicates that a previously active registration has ended and is no longer valid. + From a developer's point of view, reception of the `registration-ends` event should be treated as a signal to renew the WebRTC registration in order to continue receiving or initiating calls for the registered phone number. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.2.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: "{apiRoot}/webrtc-events/v0.2" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: Webrtc-events Subscription + description: |- + Operations to manage event subscriptions for WebRTC Event APIs. + Directly related with webrtc-call-handling and webrtc-registration. +paths: + /subscriptions: + post: + tags: + - Webrtc-events Subscription + summary: "Create a webrtc-events event subscription" + description: |- + Create a webrtc-events event subscription. For the corresponding type: + + - `org.camaraproject.webrtc-events.v0.session-invitation`: new calls event + - `org.camaraproject.webrtc-events.v0.session-status`: updates on specific call + - `org.camaraproject.webrtc-events.v0.registration-ends`: registration termination event + + To subscribe and receive notifications about new calls, a + `session-invitation` subscription is required using the `deviceId` related to a valid registration. + + operationId: createNotificationChannelSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - webrtc-events:org.camaraproject.webrtc-events.v0.session-status:create + - webrtc-events:org.camaraproject.webrtc-events.v0.session-invitation:create + - webrtc-events:org.camaraproject.webrtc-events.v0.registration-ends:create + requestBody: + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionRequest" + examples: + INVITE_SUBSCRIPTION (session-invitation): + $ref: "#/components/examples/INVITE_SUBSCRIPTION" + SESSION_SUBSCRIPTION (session-status): + $ref: "#/components/examples/SESSION_SUBSCRIPTION" + REGISTRATION_ENDS_SUBSCRIPTION (registration-ends): + $ref: "#/components/examples/REGISTRATION_ENDS_SUBSCRIPTION" + required: true + callbacks: + notifications: + "{$request.body#/sink}": + post: + summary: "notifications callback" + description: |- + Important: this endpoint is to be implemented by the API + consumer. The webrtc-events server will call this endpoint + whenever a webrtc-events event occurs. `operationId` value will + have to be replaced accordingly with WG API specific semantic. + operationId: createNotificationChannelSubscription + parameters: + - $ref: "#/components/parameters/x-correlator" + requestBody: + required: true + content: + application/cloudevents+json: + schema: + $ref: "#/components/schemas/CloudEvent" + examples: + NEW_SESSION_INCOMING (session-invitation): + $ref: "#/components/examples/NEW_SESSION_INCOMING" + SESSION_UPDATE (session-status): + $ref: "#/components/examples/SESSION_UPDATE" + REGISTRATION_EXPIRED (registration-ends): + $ref: "#/components/examples/REGISTRATION_ENDS" + SUBSCRIPTION_ENDED (subscription-ended): + $ref: "#/components/examples/SUBSCRIPTION_ENDED" + responses: + "204": + description: Successful notification + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "410": + $ref: "#/components/responses/Generic410" + "429": + $ref: "#/components/responses/Generic429" + security: + - {} + - notificationsBearerAuth: [] + + responses: + "201": + description: Created + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "202": + description: Request accepted to be processed. It applies for async creation process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/CreateSubscriptionBadRequest400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/SubscriptionPermissionDenied403" + "409": + $ref: "#/components/responses/Generic409" + "422": + $ref: "#/components/responses/CreateSubscriptionUnprocessableEntity422" + "429": + $ref: "#/components/responses/Generic429" + get: + tags: + - Webrtc-events Subscription + summary: "Retrieve a list of webrtc-events event subscription" + description: + Retrieve **a list** of webrtc-events subscription(s) with detailed + information. Including configuration data and current status. + operationId: retrieveNotificationChannelSubscriptionList + parameters: + - $ref: "#/components/parameters/x-correlator" + security: + - openId: + - webrtc-events:read + responses: + "200": + description: List of event subscription details + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + type: array + minItems: 0 + items: + $ref: '#/components/schemas/Subscription' + "400": + $ref: "#/components/responses/Generic400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + /subscriptions/{subscriptionId}: + get: + tags: + - Webrtc-events Subscription + summary: "Retrieve a webrtc-events event subscription" + description: | + Retrieve webrtc-events subscription detailed information for a given + subscription. Including configuration data and current status. + operationId: retrieveNotificationChannelSubscription + security: + - openId: + - webrtc-events:read + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "200": + description: OK + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/Subscription" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" + delete: + tags: + - Webrtc-events Subscription + summary: "Delete a webrtc-events event subscription" + operationId: deleteNotificationChannelSubscription + description: | + API endpoint to delete a given webrtc-events subscription. Action done + to stop receiving notifications about this event subscription. + security: + - openId: + - webrtc-events:delete + parameters: + - $ref: "#/components/parameters/SubscriptionId" + - $ref: "#/components/parameters/x-correlator" + responses: + "204": + description: webrtc-events subscription deleted + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + "202": + description: Request accepted to be processed. It applies for async deletion process. + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: "#/components/schemas/SubscriptionAsync" + "400": + $ref: "#/components/responses/SubscriptionIdRequired400" + "401": + $ref: "#/components/responses/Generic401" + "403": + $ref: "#/components/responses/Generic403" + "404": + $ref: "#/components/responses/Generic404" +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + notificationsBearerAuth: + type: http + scheme: bearer + bearerFormat: "{$request.body#/sinkCredential.credentialType}" + parameters: + SubscriptionId: + name: subscriptionId + in: path + description: Subscription identifier that was obtained from the create event subscription operation + required: true + schema: + $ref: "#/components/schemas/SubscriptionId" + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: A human-readable code to describe the error + message: + type: string + description: A human-readable description of what the event represents + + SubscriptionRequest: + description: The request for creating a event-type event subscription + type: object + required: + - sink + - protocol + - config + - types + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + sinkCredential: + $ref: "#/components/schemas/SinkCredential" + types: + description: |- + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: "#/components/schemas/Config" + discriminator: + propertyName: protocol + mapping: + HTTP: "#/components/schemas/HTTPSubscriptionRequest" + + Config: + description: |- + Implementation-specific configuration parameters needed by the subscription manager for acquiring + events. `subscriptionExpireTime`, `subscriptionMaxEvents`, `initialEvent` are predefined for CAMARA + specifications. + + WebRTC specific event type attributes are included into `WebrtcSubscriptionDetail` schema. + + Note: if a request is performed for several event type, all subscribed event will use same `config` + parameters. + type: object + required: + - subscriptionDetail + properties: + subscriptionDetail: + $ref: "#/components/schemas/WebrtcSubscriptionDetail" + subscriptionExpireTime: + type: string + format: date-time + example: 2023-01-17T13:18:23.682Z + description: |- + The subscription expiration time (in date-time format) requested by the API consumer. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + subscriptionMaxEvents: + type: integer + description: Identifies the maximum number of event reports to be generated (>=1) requested by the API consumer - Once this number is reached, the subscription ends. Up to API project decision to keep it. + minimum: 1 + example: 5 + initialEvent: + type: boolean + description: |- + Set to `true` by API consumer if consumer wants to get an event as soon as the subscription is created and current situation reflects event request. + Example: Consumer request Roaming event. If consumer sets initialEvent to true and device is in roaming situation, an event is triggered + Up to API project decision to keep it. + + Protocol: + type: string + enum: ["HTTP"] + description: Identifier of a delivery protocol. Only HTTP is allowed for now + example: "HTTP" + + SinkCredential: + description: A sink credential provides authentication or authorization information necessary to enable delivery of events to a target. + type: object + properties: + credentialType: + type: string + enum: + - ACCESSTOKEN + description: | + The type of the credential. + Note: Type of the credential - MUST be set to ACCESSTOKEN for now + discriminator: + propertyName: credentialType + mapping: + ACCESSTOKEN: "#/components/schemas/AccessTokenCredential" + required: + - credentialType + AccessTokenCredential: + type: object + description: An access token credential. + allOf: + - $ref: "#/components/schemas/SinkCredential" + - type: object + properties: + accessToken: + description: REQUIRED. An access token is a previously acquired token granting access to the target resource. + type: string + accessTokenExpiresUtc: + type: string + format: date-time + description: | + REQUIRED. An absolute (UTC) timestamp at which the token shall be considered expired. + In the case of an ACCESS_TOKEN_EXPIRED termination reason, implementation should notify the client before the expiration date. + If the access token is a JWT and registered "exp" (Expiration Time) claim is present, the two expiry times should match. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + accessTokenType: + description: REQUIRED. Type of the access token (See [OAuth 2.0](https://tools.ietf.org/html/rfc6749#section-7.1)). + type: string + enum: + - bearer + required: + - accessToken + - accessTokenExpiresUtc + - accessTokenType + + WebrtcSubscriptionDetail: + description: |- + The detail of the requested event subscription. + - org.camaraproject.webrtc-events.v0.session-invitation requires a + `deviceId` related to a valid registration. + - org.camaraproject.webrtc-events.v0.session-status requires a + `deviceId` related to a valid registration. + required: + - deviceId + properties: + deviceId: + type: string + format: uuid + description: |- + The device-id of the client in UUID format. A unique identifier for + the physical device where a registration is initiated. Generated + by the WebRTC application, and consistent within the same device. + + SubscriptionEventType: + type: string + description: |- + event-type - Event triggered when an event-type event occurred + - `org.camaraproject.webrtc-events.v0.session-status` + - Events triggered for any media session related event (e.g. far end new media endpoints) + - `org.camaraproject.webrtc-events.v0.session-invitation` + - Events triggered for any media endpoint registration event (e.g. incoming session) + - `org.camaraproject.webrtc-events.v0.registration-ends` + - Events triggered for registration termination (e.g. incoming session) + + `subscription-ended` is not supported for subscription. It is sent by default + enum: + - org.camaraproject.webrtc-events.v0.session-status + - org.camaraproject.webrtc-events.v0.session-invitation + - org.camaraproject.webrtc-events.v0.registration-ends + + Subscription: + description: Represents a event-type subscription. + type: object + required: + - sink + - protocol + - config + - types + - id + properties: + protocol: + $ref: "#/components/schemas/Protocol" + sink: + type: string + format: uri + pattern: ^https:\/\/.+$ + description: The address to which events shall be delivered using the selected protocol. + example: "https://endpoint.example.com/sink" + types: + description: |- + Camara Event types eligible to be delivered by this subscription. + Note: the maximum number of event types per subscription will be decided at API project level + type: array + minItems: 1 + maxItems: 1 + items: + $ref: "#/components/schemas/SubscriptionEventType" + config: + $ref: '#/components/schemas/Config' + id: + $ref: '#/components/schemas/SubscriptionId' + startsAt: + type: string + format: date-time + description: | + Date when the event subscription will begin/began + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + expiresAt: + type: string + format: date-time + description: | + Date when the event subscription will expire. Only provided when `subscriptionExpireTime` is indicated by API client or Telco Operator has specific policy about that. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2023-07-03T12:27:08.312Z" + status: + type: string + description: |- + Current status of the subscription - Management of Subscription State engine is not mandatory for now. Note not all statuses may be considered to be implemented. Details: + - `ACTIVATION_REQUESTED`: Subscription creation (POST) is triggered but subscription creation process is not finished yet. + - `ACTIVE`: Subscription creation process is completed. Subscription is fully operative. + - `INACTIVE`: Subscription is temporarily inactive, but its workflow logic is not deleted. + - `EXPIRED`: Subscription is ended (no longer active). This status applies when subscription is ended due to `SUBSCRIPTION_EXPIRED` or `ACCESS_TOKEN_EXPIRED` event. + - `DELETED`: Subscription is ended as deleted (no longer active). This status applies when subscription information is kept (i.e. subscription workflow is no longer active but its meta-information is kept). + enum: + - ACTIVATION_REQUESTED + - ACTIVE + - EXPIRED + - INACTIVE + - DELETED + discriminator: + propertyName: protocol + mapping: + HTTP: '#/components/schemas/HTTPSubscriptionResponse' + + SubscriptionAsync: + description: Response for a event-type subscription request managed asynchronously (Creation or Deletion) + type: object + properties: + id: + $ref: "#/components/schemas/SubscriptionId" + + SubscriptionId: + type: string + description: The unique identifier of the subscription in the scope of the subscription manager. When this information is contained within an event notification, this concept SHALL be referred as `subscriptionId` as per [Commonalities Event Notification Model](https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md#122-event-notification). + example: qs15-h556-rt89-1298 + + RegistrationId: + type: string + description: The unique identifier of the WebRTC registration. + example: ln3C-ttOSk-ObcQ7A0-tYO1LXqy + + CloudEvent: + description: The notification callback + required: + - id + - source + - specversion + - type + - time + properties: + id: + type: string + description: identifier of this event, that must be unique in the source context. + source: + $ref: "#/components/schemas/Source" + type: + type: string + description: |- + event-type that describes type of notification + specversion: + type: string + description: Version of the specification to which this event conforms (must be 1.0 if it conforms to cloudevents 1.0.2 version) + enum: + - "1.0" + datacontenttype: + type: string + description: 'media-type that describes the event payload encoding, must be "application/json" for CAMARA APIs' + enum: + - application/json + data: + type: object + description: |- + Event details payload. Depending of the event type, it will will include one of the data structures defined on this specification. Along with the subscription-ended, that is an authomatic event. + + Check the introduction documentation and the other CAMARA WebRTC APIs for extra info about data structures included on the events. + time: + $ref: "#/components/schemas/DateTime" + discriminator: + propertyName: "type" + mapping: + org.camaraproject.webrtc-events.v0.session-invitation: "#/components/schemas/EventSessionInvitation" + org.camaraproject.webrtc-events.v0.session-status: "#/components/schemas/EventSessionStatus" + org.camaraproject.webrtc-events.v0.subscription-ended: "#/components/schemas/EventSubscriptionEnded" + org.camaraproject.webrtc-events.v0.registration-ends: "#/components/schemas/EventRegistrationEnds" + + Source: + type: string + format: uri-reference + minLength: 1 + description: |- + Identifies the context in which an event happened - be a non-empty `URI-reference` like: + - URI with a DNS authority: + * https://github.com/cloudevents + * mailto:cncf-wg-serverless@lists.cncf.io + - Universally-unique URN with a UUID: + * urn:uuid:6e8bc430-9c3a-11d9-9669-0800200c9a66 + - Application-specific identifier: + * /cloudevents/spec/pull/123 + * 1-555-123-4567 + example: "https://notificationSendServer12.supertelco.com" + + DateTime: + type: string + format: date-time + description: |- + Timestamp of when the occurrence happened. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + example: "2018-04-05T17:31:00Z" + + ############################################ + EventSessionInvitation: + description: |- + A `org.camaraproject.webrtc-events.v0.session-invitation` event includes an specific type of session + update for new requested sessions. It is emitted when the endpoint is associated with a valid + registration and the endpoint is susbcribed to recive new incoming calls. + + This event includes all the context information: caller, callee and possible carrier data to + contextualize (call subject, branding info, etc). It MUST include a mediaSessionId, to allow the + endpoint to subscribe to this new call session. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - data + properties: + data: + $ref: "#/components/schemas/MediaSessionInvite" + type: + enum: + - org.camaraproject.webrtc-events.v0.session-invitation + + ############################################ + EventSessionStatus: + description: |- + A `org.camaraproject.webrtc-events.v0.session-status` event includes the session updates provided by + the server. This will include actions form the endpoint and the server (far end). + + In general terms, it is received each time that an event happens within the session, and include + all relevant info about the session update. + + Most common use is for SDP updates and signaling updates regarding call status. + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - mediaSessionId + - status + properties: + data: + $ref: "#/components/schemas/MediaSessionStatusUpdate" + type: + enum: + - org.camaraproject.webrtc-events.v0.session-status + + ############################################ + MediaSession: + description: |- + A prototype for media session infomration on Webrtc events. Used as event data schemas for session updates. + type: object + required: + - mediaSessionId + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + originatorAddress: + type: string + description: Sender (originator) address + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,})$' + example: 'tel:+11234567899' + originatorName: + type: string + description: Friendly name of the call originator + example: 'Alice' + receiverAddress: + type: string + description: Receiver (terminator) address + pattern: '^(tel:\+[0-9]{5,15}|sip:[A-Za-z0-9_.!%+\-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,})$' + example: 'tel:+11234567899' + receiverName: + type: string + description: Friendly name of the call terminator + example: 'Bob' + status: + type: string + description: |- + Provides the status of the media session. During the session creation, + this attribute contains 'Initial' value + example: Initial + enum: + - Initial + - InProgress + - Ringing + - Proceeding + - Connected + - Terminated + - Hold + - Resume + - SessionCancelled + - Declined + - Failed + - Waiting + - NoAnswer + - NotReachable + - Busy + offer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + answer: + $ref: '#/components/schemas/WrtcSDPDescriptor' + mediaSessionId: + type: string + description: The media session ID created by the network. The mediaSessionId shall not be included in POST requests by the client, but must be included in the notifications from the network to client. + example: '0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF' + reason: + type: string + description: The description of the event that has happened within the session + sequenceNumber: + type: integer + description: The sequence number of the notification sent to client + + MediaSessionStatusUpdate: + allOf: + - $ref: "#/components/schemas/MediaSession" + - type: object + description: MediaSession information emitted on a EventSessionStatus event + required: + - status + + MediaSessionInvite: + allOf: + - $ref: "#/components/schemas/MediaSession" + - type: object + description: MediaSession information emitted on a EventSessionInvitation event + required: + - originatorAddress + - receiverAddress + - status + + WrtcSDPDescriptor: + type: object + properties: + sdp: + type: string + description: |- + An inlined session description in SDP format [RFC4566].If XML syntax is used, the content of this element SHALL be embedded in a CDATA section + + # CloudEvent and CAMARA standard + EventSubscriptionEnded: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + properties: + data: + $ref: "#/components/schemas/SubscriptionEnded" + type: + enum: + - org.camaraproject.webrtc-events.v0.subscription-ended + + SubscriptionEnded: + description: Event detail structure for SUBSCRIPTION_ENDED event + type: object + required: + - subscriptionId + - terminationReason + properties: + subscriptionId: + $ref: "#/components/schemas/SubscriptionId" + terminationReason: + $ref: "#/components/schemas/TerminationReason" + terminationDescription: + type: string + + TerminationReason: + type: string + description: |- + - NETWORK_TERMINATED - API server stopped sending notification + - SUBSCRIPTION_EXPIRED - Subscription expire time (optionally set by the requester) has been reached + - MAX_EVENTS_REACHED - Maximum number of events (optionally set by the requester) has been reached + - ACCESS_TOKEN_EXPIRED - Access Token sinkCredential (optionally set by the requester) expiration time has been reached + - SUBSCRIPTION_DELETED - Subscription was deleted by the requester + enum: + - MAX_EVENTS_REACHED + - NETWORK_TERMINATED + - SUBSCRIPTION_EXPIRED + - ACCESS_TOKEN_EXPIRED + - SUBSCRIPTION_DELETED + + # WebRTC Registration Ends event + EventRegistrationEnds: + description: event structure for event subscription ends + allOf: + - $ref: "#/components/schemas/CloudEvent" + - type: object + required: + - data + properties: + data: + $ref: "#/components/schemas/RegistrationEnds" + type: + enum: + - org.camaraproject.webrtc-events.v0.registration-ends + + RegistrationEnds: + description: Event detail structure for REGISTRATION_ENDS event. registrationExpireTime is absolute UTC. Clients SHOULD refresh in advance; otherwise a REGISTRATION_EXPIRED terminationReason will be emitted. + type: object + required: + - registrationId + - terminationReason + properties: + registrationId: + $ref: "#/components/schemas/RegistrationId" + terminationDescription: + type: string + terminationReason: + $ref: "#/components/schemas/RegistrationTerminationReason" + + RegistrationTerminationReason: + type: string + description: |- + - NETWORK_TERMINATED - API server stopped sending notification + - REGISTRATION_EXPIRED - Registration expire time (optionally set by the requester) has been reached. REGISTRATION_EXPIRED is triggered exactly when the set registrationExpireTime has passed. + enum: + - NETWORK_TERMINATED + - REGISTRATION_EXPIRED + + HTTPSubscriptionRequest: + allOf: + - $ref: "#/components/schemas/SubscriptionRequest" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSubscriptionResponse: + allOf: + - $ref: "#/components/schemas/Subscription" + - type: object + properties: + protocolSettings: + $ref: "#/components/schemas/HTTPSettings" + + HTTPSettings: + type: object + properties: + headers: + type: object + description: |- + A set of key/value pairs that is copied into the HTTP request as custom headers. + + NOTE: Use/Applicability of this concept has not been discussed in Commonalities under the scope of Meta Release v0.4. When required by an API project as an option to meet a UC/Requirement, please generate an issue for Commonalities discussion about it. + additionalProperties: + type: string + method: + type: string + description: The HTTP method to use for sending the message. + enum: + - POST + + responses: + CreateSubscriptionBadRequest400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - INVALID_PROTOCOL + - INVALID_CREDENTIAL + - INVALID_TOKEN + - INVALID_SINK + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_INVALID_PROTOCOL: + description: Invalid protocol for events subscription management + value: + status: 400 + code: INVALID_PROTOCOL + message: Only HTTP is supported + GENERIC_400_INVALID_CREDENTIAL: + description: Invalid sink credential type + value: + status: 400 + code: INVALID_CREDENTIAL + message: Only Access token is supported + GENERIC_400_INVALID_TOKEN: + description: Invalid token type for sink credential of type ACCESSTOKEN + value: + status: 400 + code: INVALID_TOKEN + message: Only bearer token is supported + GENERIC_400_INVALID_SINK: + description: Invalid sink value + value: + status: 400 + code: INVALID_SINK + message: sink not valid for the specified protocol + Generic400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + SubscriptionIdRequired400: + description: Problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_SUBSCRIPTION_ID_REQUIRED: + description: subscription id is required + value: + status: 400 + code: INVALID_ARGUMENT + message: "Expected property is missing: subscriptionId" + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + SubscriptionPermissionDenied403: + description: Client does not have sufficient permission + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - SUBSCRIPTION_MISMATCH + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_SUBSCRIPTION_MISMATCH: + description: Inconsistent access token for requested subscription + value: + status: 403 + code: "SUBSCRIPTION_MISMATCH" + message: "Inconsistent access token for requested events subscription" + Generic404: + description: Resource Not Found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + Generic409: + description: Conflict + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 409 + code: + enum: + - ABORTED + - ALREADY_EXISTS + examples: + GENERIC_409_ABORTED: + description: Concurreny of processes of the same nature/scope + value: + status: 409 + code: ABORTED + message: Concurrency conflict. + GENERIC_409_ALREADY_EXISTS: + description: Trying to create an existing resource + value: + status: 409 + code: ALREADY_EXISTS + message: The resource that a client tried to create already exists. + Generic410: + description: Gone + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 410 + code: + enum: + - GONE + examples: + GENERIC_410_GONE: + description: Use in notifications flow to allow API Consumer to indicate that its callback is no longer available + value: + status: 410 + code: GONE + message: Access to the target resource is no longer available. + CreateSubscriptionUnprocessableEntity422: + description: Unprocessable Entity + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 422 + code: + enum: + - SERVICE_NOT_APPLICABLE + - MISSING_IDENTIFIER + - UNSUPPORTED_IDENTIFIER + - UNNECESSARY_IDENTIFIER + - MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + - MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED + examples: + GENERIC_422_SERVICE_NOT_APPLICABLE: + description: Service not applicable for the provided identifier + value: + status: 422 + code: SERVICE_NOT_APPLICABLE + message: The service is not available for the provided identifier. + GENERIC_422_MISSING_IDENTIFIER: + description: An identifier is not included in the request and the device or phone number identification cannot be derived from the 3-legged access token + value: + status: 422 + code: MISSING_IDENTIFIER + message: The device cannot be identified. + GENERIC_422_UNSUPPORTED_IDENTIFIER: + description: None of the provided identifiers is supported by the implementation + value: + status: 422 + code: UNSUPPORTED_IDENTIFIER + message: The identifier provided is not supported. + GENERIC_422_UNNECESSARY_IDENTIFIER: + description: An explicit identifier is provided when a device or phone number has already been identified from the access token + value: + status: 422 + code: UNNECESSARY_IDENTIFIER + message: The device is already identified by the access token. + GENERIC_422_MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED: + description: Multi event types subscription is not supported + value: + status: 422 + code: MULTIEVENT_SUBSCRIPTION_NOT_SUPPORTED + message: Multi event types subscription not managed + GENERIC_422_MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED: + description: Combination of multiple event types is temporarily not supported + value: + status: 422 + code: MULTIEVENT_COMBINATION_TEMPORARILY_NOT_SUPPORTED + message: The requested combination of event types is temporarily not supported. + Generic429: + description: Too Many Requests + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 429 + code: + enum: + - QUOTA_EXCEEDED + - TOO_MANY_REQUESTS + examples: + GENERIC_429_QUOTA_EXCEEDED: + description: Request is rejected due to exceeding a business quota limit + value: + status: 429 + code: QUOTA_EXCEEDED + message: Out of resource quota. + GENERIC_429_TOO_MANY_REQUESTS: + description: Access to the API has been temporarily blocked due to rate or spike arrest limits being reached + value: + status: 429 + code: TOO_MANY_REQUESTS + message: Rate limit reached. + examples: + # Subscription examples + REGISTRATION_ENDS_SUBSCRIPTION: + description: |- + A sample of `registration-ends` subscription for registrationId + `+xsmcaum3z4zw4l0cu4w115m0` at `acme.opentelco.com`. + + This will be used to receive WebRTC registration termination events + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + sinkCredential: + credentialType: "ACCESSTOKEN" + accessToken: "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiL.." + accessTokenExpireUtc: "2024-12-06T14:37:56.147Z" + accessTokenType: "bearer" + types: + - org.camaraproject.webrtc-events.v0.registration-ends + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + INVITE_SUBSCRIPTION: + description: |- + A sample of media `session-invitation` subscription for phone number + `+1234567890` at `acme.opentelco.com`. + + This will be used to receive incoming sessions (incoming + calls). The implicit subscription to `subscription-ended` will make + the client aware of registration status updates from the server. + (i.e. when a REGISTRATION expires). + + The provided example will be able to receive up to 50 calls until + subscription is cancelled via server or by configuration timeout. Check + callback examples to check some possible events received: + + - New incoming call + - Registration revoked + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + types: + - org.camaraproject.webrtc-events.v0.session-invitation + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + initialEvent: true + subscriptionMaxEvents: 50 + subscriptionExpireTime: "2024-11-17T13:18:23.682Z" + SESSION_SUBSCRIPTION: + description: |- + A sample of media `session-status` subscription for a specific + `mediaSessionId` at `acme.opentelco.com`. + + Identified by for `mediaSessionId`, and validated via a `registrationId` + the endpoint is able to interact with its own media session. + This could be used to remotely control the call or to handle the async + session establishment. For instance, updating the user interface for + different statuses: InProgress, Ringing, Cancel, etc. + value: + protocol: HTTP + sink: https://notificationServer.opentelco.com + types: + - org.camaraproject.webrtc-events.v0.session-status + config: + subscriptionDetail: + deviceId: "7d444840-9dc0-11d1-b245-5ffdce74fad2" + initialEvent: true + subscriptionMaxEvents: 50 + subscriptionExpireTime: "2024-11-17T13:18:23.682Z" + # Event examples + NEW_SESSION_INCOMING: + description: |- + Example of `session-invitation` event. + + A new media session is requested (i.e. incoming call). This event + starts a session negotiation. All other events related with this + media session will be shared via the `session-status` events, and + identified via the unique `mediaSessionId`. + + The main point to distinguish between a *new session* and an update over + an *existing session* is the **type**. A `session-invitation` describes + on its content, all information required to initiate a new voice-video call. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.session-invitation + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: "qs15-h556-rt89-1298" + originatorAddress: "tel:+11234567899" + originatorName: "Alice" + receiverAddress: "tel:+11234998765" + receiverName: "Bob" + status: "Initial" + offer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0" + mediaSessionId: "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" + reason: "New subscriber incoming call" + sequenceNumber: 1 + REGISTRATION_ENDS: + description: |- + Example of `registration-ends` events. + + This scenario occurs when the device did not refresh before the registration expiry time (registrationExpireTime). + When a re-registration is requested from server, maybe due to expire or + administrative token revocation or due any other technical reason. It + is expected from the endpoint to re-register. No new sessions will be + delivered to the user endpoint, as the subscription is not valid + anymore. + + Here, an example of how the network will communicate to the client that + the registration is not valid anymore, detailing on + `terminationDescription` the root cause of the registration removal. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.registration-ends + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: qs15-h556-rt89-1298 + registrationId: xsmcaum3z4zw4l0cu4w115m0 + terminationReason: REGISTRATION_EXPIRED + terminationDescription: "SIP re-registration required" + SESSION_UPDATE: + description: |- + Example of `session-status` events. + + Session status events are produced when there is an update on the + session status, due changes on the signaling status of the call (eg.: + InProgress, Ringing, Proceeding, Connected, Terminated, ...) or due + SDP changes on any involved party. + + This example, presents an SDP update due change on call status (to + Progress) and including answer SDP data. Customer client now, can + establish a voice-video channel and start transmitting and receiving + media. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.session-status + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: "qs15-h556-rt89-1298" + originatorAddress: "tel:+11234567899" + originatorName: "Alice" + receiverAddress: "tel:+11234998765" + receiverName: "Bob" + status: InProgress + offer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + answer: + sdp: "v=0\r\no=- 4576312012535546667 4 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\nm=audio 47510 RTP/SAVPF 102 113\r\nc=IN IP6 2001:e0:410:243a:a344:cee7:7b39:bb1e\r\nb=AS:64\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:3108871805 1 udp 2122262783 2001:e0:410:243a:a344:cee7:7b39:bb1e 47510 typ host generation 0 network-id 3 network-cost 900\r\na=ice-ufrag:47Nx\r\na=ice-pwd:ln3CttOSkObcQ7A0tYO1LXqy\r\na=ice-options:trickle renomination\r\na=mid:audio\r\na=extmap:2 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=sendrecv\r\na=rtcp-mux\r\na=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:ruAnBNYnTJqDVZAIJV59VpQ5DxGI6tMX9h9kkHSz\r\na=rtpmap:102 AMR-WB/16000\r\na=fmtp:102 octet-align=0; mode-set=0,1,2; mode-change-capability=2\r\na=rtpmap:113 telephone-event/16000\r\na=ptime:20\r\n" + mediaSessionId: "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" + reason: "Answer SDP update" + sequenceNumber: 3 + SUBSCRIPTION_ENDED: + description: |- + Example of `subscription-ended` events. + + Triggered when an event subscription is not valid anymore. Maybe due + administrative token revocation or due any other technical reason. It + is expected from the endpoint to subscribe again. No new events will be + delivered to the user endpoint, as the subscription is not valid + anymore. + + Here, an example of how the network will communicate to the client that + the subscription is not valid anymore, detailing on + `terminationDescription` the root cause of the subscription remove. + value: + id: "VzYQCOClM6Kc7Xmyq7mP58Jx" + source: https://notificationServer.opentelco.com + type: org.camaraproject.webrtc-events.v0.subscription-ended + specversion: "1.0" + datacontenttype: application/json + time: 2024-11-05T05:40:23.682Z + data: + subscriptionId: qs15-h556-rt89-1298 + terminationReason: SUBSCRIPTION_EXPIRED + terminationDescription: "Subscription expired" diff --git a/original/WebRTC/code/API_definitions/webrtc-registration.yaml b/original/WebRTC/code/API_definitions/webrtc-registration.yaml new file mode 100644 index 0000000000000000000000000000000000000000..b0b01f55ce60dc1dd7260042446b44414468db0e --- /dev/null +++ b/original/WebRTC/code/API_definitions/webrtc-registration.yaml @@ -0,0 +1,609 @@ +openapi: 3.0.3 +info: + title: WebRTC Registration Service + description: |- + # Introduction + This API provides the API consumer with the capabilities to manage + registration and connectivity towards the network. + + The network requires that the API consumer application registers and + identifies an end user device before enabling any media + session services provided by the WebRTC APIs. + + A device registration created via this API will register a unique `deviceId` + created by the API consumer (WebRTC application) and it will will provide a + `registrationId` to manage a registration later. + Any subsequent request from the API consumer must include the unique + `registrationId` that will be linked to the registration previously defined. + + All operator network services are based on device registrations, this API + allows the user to create a registration session that enable the audio/video + functionalities exposed by the operator network. + + **Use cases to cover:** + - Functional: + - Ability to create Registration sessions on the network, this grants + access to create new audio and video sessions. + - Ability to update or remove Registration sessions on the network + - An additional subscription to webrtc-events API is required to receive + incoming calls. + + # Relevant terms and definitions + + - **registration** A media device session. A valid client running on a valid + device, with permission to use the network capabilities to create and receive + (audio/video) calls (media sessions). + - **registrationId**: Unique identifier of an WebRTC device **registration**. + Retrieved using the `webrtc-registration` API + - **deviceId**: A unique identifier for the physical device where a media + session is initiated. It is provided by the WebRTC application, it remains + consistent across multiple installations or logins on the same device. Its + primary function is to ensure that only one WebRTC session (**registration**) + is active per device at a time, enabling the gateway to clean up any stale + sessions if a new session is initiated on the same device. + - **media session**: An exchange of media between devices. + Typical example of session is a "single one-to-one call". + - **mediaSessionId**: Unique identifier of a Voice or Video **session** using + webrtc-call-handling API. Retrieved using the `webrtc-call-handling` API + - **x-correlator**: Unique ID included in the API request created by the API consumer. + It is used to correlate an API request with its response and help in debugging. + - **WebRTC**: WebRTC is a free and open-source project providing web browsers + and mobile applications with real-time communication via application programming + interfaces. It allows audio and video communication and streaming to work + inside web pages by allowing direct peer-to-peer communication + - **SDP**: Acronym for Session Description Protocol. The SDP is a format for + describing multimedia communication sessions for the purposes of announcement + and invitation. + + # API functionality + + This API allows to create device registrations. These, identified by a unique + `registrationId` can be updated and terminated via this API and its methods. + - **POST**: Create a new device registration using a valid authorization token. + - **PUT**: Update a device registration via its unique `registrationId` + - **DELETE**: Finish an existing device registration via its unique `registrationId` + To receive server-side updates about new voice-video sessions, you need to + use `webrtc-events` API. + + The main concept of the API is pretty straightforward: a subscriber needs a + session to create calls, so you will need a subscription on your device before + attempt any audio/video call. + + Once you create a session, you can: + - Use `webrtc-events` API to create a subscription and receive incoming calls. + - Use `webrtc-call-handling` API to create a audio/video session and create + an outgoing call. + + Check for extra details on each of these APIs already present on the WebRTC + repository. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an + API consumer requests an access token. Please refer to Identity and Consent + Management (https://github.com/camaraproject/IdentityAndConsentManagement/) + for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the + onboarding process, happening between the API consumer and the API provider, + taking into account the declared purpose for accessing the API, whilst also + being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise + their rights through mechanisms such as opt-in and/or opt-out, the use of + three-legged access tokens is mandatory. This ensures that the API remains + in compliance with privacy regulations, upholding the principles of + transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. + Therefore the API specification may not document some non-mandatory error + statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release + associated to this API version for a complete list of error responses. The + applicable Commonalities Release can be identified in the `API Readiness + Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible + error response if it is explicitly documented in the API. + + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html + version: 0.3.0 + x-camara-commonalities: 0.6 + +externalDocs: + description: Product documentation at CAMARA + url: https://github.com/camaraproject/WebRTC +servers: + - url: '{apiRoot}/webrtc-registration/v0.3' + description: APIs to manage device registration and connection + variables: + apiRoot: + description: API Root + default: http://localhost:9091 +tags: + - name: Registration + description: Operations to manage device registration with the network +paths: + /sessions: + post: + tags: + - Registration + summary: Create a registration + description: |- + API endpoint used to create a new registration of a device in the network. + It uses the `deviceId` in the request body. + In response, a `registrationId` (in UUID format) is provided to identify + this device registration within the network. + operationId: createRegistration + parameters: + - $ref: '#/components/parameters/x-correlator' + security: + - openId: + - webrtc-registration:sessions:create + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionRequest' + responses: + '200': + description: Ok + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionResponse' + '400': + $ref: "#/components/responses/CreateSessionBadRequest400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/CreateSessionForbidden403" + /sessions/{registrationId}: + put: + tags: + - Registration + summary: Refresh network registration. + description: |- + API endpoint used to **refresh** an existing registration *before* it + expires. + + **Server behaviour on refresh** + + 1. Let `t_req` be the server-side receipt time of the request and + `t_prev` the previously stored `registrationExpireTime`. + 2. Compute the remaining lifetime + remaining = t_prev - t_req + (values ≤ 0 indicate the client is late; operators MAY reject or + treat it as a new registration). + 3. Apply the operator's configured TTL (`TTL_cfg`, e.g. 3600 s) **from + `t_req`, not from `t_prev`**: + newExpire = t_req + TTL_cfg + 4. Persist `newExpire` and return it in `expiresAt` inside the + response body. + + Clients SHOULD plan to refresh well **before** `newExpire` to avoid + race conditions. + operationId: updateRegistrationById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamRegistrationId' + security: + - openId: + - webrtc-registration:sessions:write + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionUpdate' + responses: + '200': + description: Ok + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + $ref: '#/components/schemas/regSessionResponse' + '204': + description: Updated the registration status (no content) + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: "#/components/responses/Generic400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/Generic403" + '404': + $ref: '#/components/responses/Generic404' + delete: + tags: + - Registration + summary: Delete Registration Session. + description: |- + API endpoint used to remove a valid registration on the network. This action + frees any resource and invalidates future actions that involves this + registration between the device and the network. + + Use the registrationId to identify the registration to delete. + operationId: deleteRegistrationById + parameters: + - $ref: '#/components/parameters/x-correlator' + - $ref: '#/components/parameters/pathParamRegistrationId' + security: + - openId: + - webrtc-registration:sessions:delete + responses: + '204': + description: No Content + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + '400': + $ref: "#/components/responses/Generic400" + '401': + $ref: "#/components/responses/Generic401" + '403': + $ref: "#/components/responses/Generic403" + '404': + $ref: '#/components/responses/Generic404' +components: + securitySchemes: + openId: + type: openIdConnect + openIdConnectUrl: https://example.com/.well-known/openid-configuration + headers: + x-correlator: + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + $ref: "#/components/schemas/XCorrelator" + pathParamRegistrationId: + name: registrationId + in: path + description: The registrationId assigned by the registration service + required: true + style: simple + explode: false + schema: + type: string + schemas: + XCorrelator: + type: string + pattern: ^[a-zA-Z0-9-_:;.\/<>{}]{0,256}$ + example: "b4333c46-49c0-4f62-80d7-f0ef930f1c46" + regSessionRequest: + type: object + required: + - deviceId + properties: + deviceId: + type: string + pattern: uuid + description: |- + The deviceId of the client in UUID format. A unique identifier for + the physical device where a registration is initiated. Generated + by the WebRTC application, and consistent within the same device. + registrationExpireTime: + type: string + format: date-time + description: |- + Optional **absolute** expiry moment for this registration. + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + + ▸ **Devices without a trustworthy clock** (e.g. Wi-Fi-only tablets + or other non-SIM hardware) SHOULD treat the value as an + **upper bound**. Such devices MAY derive a local time-to-live: + + ttl = registrationExpireTime - now() + + and initiate a refresh *before* `ttl` elapses (a safety margin + of ~120 s is recommended). + + ▸ If the client omits this field, the server will set the expiry + according to its own TTL policy and return the resulting + `registrationExpireTime` in the response. + regSessionResponse: + type: object + required: + - registrationId + properties: + regInfo: + $ref: '#/components/schemas/RegistrationInformation' + registrationId: + type: string + description: The registration session ID is returned when registering a device with the network . Clients must utilize this ID to as a parameter in the call-handling and subscription APIs. + expiresAt: + type: string + format: date-time + description: |- + Authoritative expiry timestamp calculated **after** applying the + refresh logic. Clients MUST treat this value as the new upper-bound + and schedule their next refresh accordingly. + + Client applications should compute the remaining time before expiry (expiresAt - currentTime) + and plan to refresh well in advance to avoid race conditions. A suggested margin is 120 seconds before expiry. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + regSessionUpdate: + type: object + properties: + registrationExpireTime: + type: string + format: date-time + description: |- + Optional **absolute** UTC timestamp that *requests* a new expiry. + The server will honour the value only if it is **later than the + operator's minimum TTL** and **earlier than operator maximum TTL**; + otherwise it falls back to its own policy (see refresh algorithm + above). + + If omitted, the server always extends the expiry by its configured + TTL, measured from the moment the refresh is received. + + It must follow [RFC 3339](https://datatracker.ietf.org/doc/html/rfc3339#section-5.6) and must have time zone. + RegistrationStatus: + type: string + enum: + - Registered + RegistrationInformation: + type: object + properties: + phoneNumber: + $ref: '#/components/schemas/PhoneNumber' + regStatus: + $ref: '#/components/schemas/RegistrationStatus' + ErrorInfo: + type: object + required: + - status + - code + - message + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Friendly Code to describe the error + message: + type: string + description: A human readable description of what the event represent + PhoneNumber: + description: A public identifier addressing a telephone subscription. In mobile networks it corresponds to the MSISDN (Mobile Station International Subscriber Directory Number). In order to be globally unique it has to be formatted in international format, according to E.164 standard, prefixed with '+'. + type: string + pattern: '^\+[1-9][0-9]{4,14}$' + example: "+123456789" + + responses: + # Method specific responses + CreateSessionBadRequest400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + - EMERGENCY_ADDRESS_MISSING + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + GENERIC_400_EMERGENCY_ADDRESS_MISSING: + description: Specific Syntax Exception regarding emergency address that is relevant in the context of the API + value: + status: 400 + code: EMERGENCY_ADDRESS_MISSING + message: Emergency address missing + CreateSessionForbidden403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + - MAX_REGISTRATION_PER_USER + - MAX_REGISTRATION_PER_MSISDN + - MAX_DEVICES_PER_USER + examples: + CREATE_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + CREATE_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "device is not consistent with access token." + CREATE_403_MAX_REGISTRATION_PER_USER: + # summary: Max registration per user + value: + status: 403 + code: MAX_REGISTRATION_PER_USER + message: 'The maximum number of service registrations per user has been reached' + CREATE_403_MAX_REGISTRATION_PER_MSISDN: + # summary: Max registration per MSISDN + value: + status: 403 + code: MAX_REGISTRATION_PER_MSISDN + message: 'The maximum number of service registrations per MSISDN has been reached' + CREATE_403_MAX_DEVICES_PER_USER: + # summary: Max devices per user + value: + status: 403 + code: MAX_DEVICES_PER_USER + message: 'The maximum number of device instances per user has been reached' + # Generic responses + Generic400: + description: Bad Request + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 400 + code: + enum: + - INVALID_ARGUMENT + - OUT_OF_RANGE + examples: + GENERIC_400_INVALID_ARGUMENT: + description: Invalid Argument. Generic Syntax Exception + value: + status: 400 + code: INVALID_ARGUMENT + message: Client specified an invalid argument, request body or query param. + GENERIC_400_OUT_OF_RANGE: + description: Out of Range. Specific Syntax Exception used when a given field has a pre-defined range or a invalid filter criteria combination is requested + value: + status: 400 + code: OUT_OF_RANGE + message: Client specified an invalid range. + Generic401: + description: Unauthorized + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 401 + code: + enum: + - UNAUTHENTICATED + examples: + GENERIC_401_UNAUTHENTICATED: + description: Request cannot be authenticated and a new authentication is required + value: + status: 401 + code: UNAUTHENTICATED + message: Request not authenticated due to missing, invalid, or expired credentials. A new authentication is required. + Generic403: + description: Forbidden + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 403 + code: + enum: + - PERMISSION_DENIED + - INVALID_TOKEN_CONTEXT + examples: + GENERIC_403_PERMISSION_DENIED: + description: Permission denied. OAuth2 token access does not have the required scope or when the user fails operational security + value: + status: 403 + code: PERMISSION_DENIED + message: Client does not have sufficient permissions to perform this action. + GENERIC_403_INVALID_TOKEN_CONTEXT: + description: Reflect some inconsistency between information in some field of the API and the related OAuth2 Token + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + message: "{{field}} is not consistent with access token." + Generic404: + description: Not found + headers: + x-correlator: + $ref: "#/components/headers/x-correlator" + content: + application/json: + schema: + allOf: + - $ref: "#/components/schemas/ErrorInfo" + - type: object + properties: + status: + enum: + - 404 + code: + enum: + - NOT_FOUND + - IDENTIFIER_NOT_FOUND + examples: + GENERIC_404_NOT_FOUND: + description: Resource is not found + value: + status: 404 + code: NOT_FOUND + message: The specified resource is not found. + GENERIC_404_IDENTIFIER_NOT_FOUND: + description: Some identifier cannot be matched to a device + value: + status: 404 + code: IDENTIFIER_NOT_FOUND + message: Device identifier not found. diff --git a/original/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist.md b/original/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..130fc48ebfb53cbbeb018328a38bcd75b2b6fb92 --- /dev/null +++ b/original/WebRTC/documentation/API_documentation/webrtc-call-handling-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API WebRTC Call Handling + +Checklist for webrtc-call-handling v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-call-handling.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/original/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist.md b/original/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..ab9383934019620e0b904fe5856b9175526664e6 --- /dev/null +++ b/original/WebRTC/documentation/API_documentation/webrtc-events-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API WebRTC events + +Checklist for webrtc-events v0.2.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-events.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/original/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist.md b/original/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist.md new file mode 100644 index 0000000000000000000000000000000000000000..7a27c7ee64fce8e75fbbfbb3b801017d55666f95 --- /dev/null +++ b/original/WebRTC/documentation/API_documentation/webrtc-registration-API-Readiness-Checklist.md @@ -0,0 +1,19 @@ +# API WebRTC Registration + +Checklist for webrtc-registration v0.3.0 in r2.2 + +| Nr | API release assets | alpha | release-candidate | initial
                                                                                public | stable
                                                                                public | Status | Reference information | +|----|----------------------------------------------|:-----:|:-----:|:-----:|:-----:|:-----:|:-----:| +| 1 | API definition | M | M | M | M | Y | [link](/code/API_definitions/webrtc-registration.yaml) | +| 2 | Design guidelines from Commonalities applied | O | M | M | M | Y | r3.3 | +| 3 | Guidelines from ICM applied | O | M | M | M | Y | r3.3 | +| 4 | API versioning convention applied | M | M | M | M | Y | | +| 5 | API documentation | M | M | M | M | Y | inline in YAML | +| 6 | User stories | O | O | O | M | N | | +| 7 | Basic API test cases & documentation | O | M | M | M | Y | [link](/code/Test_definitions/) | +| 8 | Enhanced API test cases & documentation | O | O | O | M | N | | +| 9 | Test result statement | O | O | O | M | N | | +| 10 | API release numbering convention applied | M | M | M | M | Y | | +| 11 | Change log updated | M | M | M | M | Y | [link](/CHANGELOG.md) | +| 12 | Previous public release was certified | O | O | O | M | N | | +| 13 | API description (for marketing) | O | O | M | M | Y | [wiki link](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/81101647/WebRTC+API+description) | diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_231023.md b/original/WebRTC/documentation/MeetingMinutes/MoM_231023.md new file mode 100644 index 0000000000000000000000000000000000000000..58b85dd0743a6aa53056dd0c02d05774b01b5ff7 --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_231023.md @@ -0,0 +1,56 @@ +# MoM - WebRTC Working group - 231023 + +**Date:** 23/oct/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Cristina Santana (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santiago Troncoso (Quobis) +* Elías Pérez (Quobis) +* Jesus Pedruelo (Vodafone) +* Maxime Delon (Orange) + +## Agenda + +1. Welcome participants +2. Time slot approval +3. API Background +4. Scope definition: +
                                                                                • Technical Scope +
                                                                                • Task management
                                                                                +5. Roles definition (CODEOWNERS, MAINTAINERS) + + +## Discussion + +TMUS/Deepak : not to focus only on simple use cases and be concerned always that the API needs to be evolved to complex ones. +TMUS/Deepak : The current version of the API does not support choosing the line to be used for registration. It retrieves the MSISDN based on the deviceid provided by the client. The comment was to update the API to support selecting the line to be registered. +TMUS/Deepak : Notification channel – current version assumes websocket to be the only notification channel, the comment was to support multiple notification channel i.e. websocket, pns and web hooks. +Focus initially on the proposed use case to develop later - the initial version should be extensible to support any future changes. +The delivery UNI will initially be done thorugh JSON over websockets. +The NBI will be API REST. + +| Item | Who | Description | +| ---- | --- | ----------- | +| Time slot for the repetitions | webRTC WG| Aproved: Mondays 8am CET each 15 days. | +|Functional Scope aproval| webRTC WG| Aproved:
                                                                                Enable web endpoints (clients) to register, receive and make calls through an UNI API based on the OIDC FE flow. Then the functional scope for the API is:
                                                                                • Enable a web endpoint to register for IMS services through a webRTC Gateway using Oauth 2.0 and the Operator provided Identity Provider (IDP)
                                                                                • Open webSockets to receive IMS call events using JSON for the delivery
                                                                                • Make calls from the endpoint (client) side by establishing WebSocket using the channel URL received as part of the registration procedure.
                                                                                For this Scope two separated API are proposed:
                                                                                • One API for REST clients for 1-1 calling (CALL HANDLING)
                                                                                • One API for clients to manage Registration and Connectivity (RACM) towards MNO's IMS Network (REGISTRATION AND CONNECTIVITY MANAGEMENT)
                                                                                | +|Proposed Roles| webRTC WG | CODE OWNERS:
                                                                                • Ricardo Serrano: @TEF-RicardoSerr
                                                                                • Sushanth Hegde: @sushanthmavenir
                                                                                • Pradeep Achar Pushpa: @pradeepachar-mavenir
                                                                                MAINTAINERS:
                                                                                • Rafał Artych: @rartych
                                                                                • Deepak Jaiswal: @deepakjaiswal1
                                                                                • Santiago Troncoso: @stroncoso-quobis
                                                                                • Elías Pérez: @eliaspc
                                                                                • Jesus Pedruelo: @jesus-pb
                                                                                • Ratna Ratnanandan: @ratnavf
                                                                                • Benjamin Busvel: @BenjaminBusvel 
                                                                                | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Create the first PR with the two proposed seed YAML documents:
                                                                                • CallHandling-Service
                                                                                • RACM-Service| Ricardo Serrano| +| 2. Evaluate the accomodation of notifications to the webclient in the API Flow and bring a proposal for the nov/6th meeting | Sushanth Hegde | +| 3. Create a new issue "Notifications integration" to give ofline follow-up to Sushanth with his action point | Ricardo Serrano | +| 4. Update the repository information (maintainers, scope, codeowners etc.) | Ricardo Serrano | + +## AOB +* Next meeting will be the 6th of november diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_231106.md b/original/WebRTC/documentation/MeetingMinutes/MoM_231106.md new file mode 100644 index 0000000000000000000000000000000000000000..acb356793cc04b878577ee7f93de76c1d78f1d4d --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_231106.md @@ -0,0 +1,47 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 06/nov/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* David Moro (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Elías Pérez (Quobis) + +## Agenda + +1. Previous meeting minutes aproval +2. Notifications flow discussion +3. Identity providing + * Parameters handling (userID and deviceID) + * Line selection + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | Aproved | +| Notifications flow discussion | WebRTC WG | As stated in the previous meeting, there should be a third API specification file defined specifically for the Notification channel. Sushanth came up with the YAML specification and will be PR-ed by today.
                                                                                  For now it only supports Websockets but in the future it may support other channel types.  | +| Parameters handling (userID and deviceID) | WebRTC WG | The userID will be the telco IdP token.
                                                                                  The deviceID will be the unique device identifyer.
                                                                                  • Regarding multitabs in browsers, there will not be provided new identities to each of the tabs as there will be multiple ringing (undesired behaviour) | +| Line selection | WebRTC WG | To close the issue as it is agreed that the line selection should be done outside the API scope.
                                                                                    Anyhow, it is needed to see the end to end API to clarify this point | +| Error handling | WebRTC WG | Error handling should be taken into account and it need to be definded what to do in cases when the user do not have a line (error to be handled by the IdP) or state if there is needed to state a limit on registered lines for a user | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Close line selection issue opened | Ricardo Serrano | +| 2. Make the first contribution for the documentation of the API in markdown format | Sushanth Hegde | +| 3. Make the PR of the notification channel specification | Sushanth Hegde | +| 4. Make first proposal on Error Handling in the new Issue created | Deepak Jaiswal | +| 5. Review uploaded files on CAMARA, check the format and provide comments | All | + +## AOB + +* Next meeting will be the 20th of november diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_231120.md b/original/WebRTC/documentation/MeetingMinutes/MoM_231120.md new file mode 100644 index 0000000000000000000000000000000000000000..11e56790d421a32cf759950e1f9046fd0316b7fe --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_231120.md @@ -0,0 +1,51 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 20/nov/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* David Moro (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santiago Troncoso (Quobis) +* Jesus Pedruelo (Vodafone) + +## Agenda + + +1. Previous meetings approval: Minutes of Meeting 231106 by TEF-RicardoSerr · [Pull Request #8](https://github.com/camaraproject/WebRTC/pull/8) · camaraproject/WebRTC · GitHub +2. Notification issue and PR comments discussion: Updated yaml files by pradeepachar-mavenir · [Pull Request #6](https://github.com/camaraproject/WebRTC/pull/6) · camaraproject/WebRTC · GitHub +3. Next steps (documentation) + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | To be Aproved | +| Notifications flow discussion | WebRTC WG |
                                                                                    • T-Mobile sugests to keep the notification system method in a separate channel and only send to the API endpoint the content of the notification system. Also sugest to follow the OMA standard for API definition.
                                                                                    • Telefonica concerns about PNS channels not being supported and the structure of the API itself.
                                                                                    • Mavenir commit to update the YAMLs having this two bullets into account
                                                                                    • The first sequence would be to create the notification channel and the second sequence would be to do the registration | +Others | WebRTC WG|
                                                                                      • The operators have internal credentials which are the ones to be used in the registration process in the API (Telco IdP would provide the Token)
                                                                                      • Quobis recommends making it clear in the documentation that the authentication process will be done via Oauth. | + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Error Analysis, [issue #7](https://github.com/camaraproject/WebRTC/issues/7) | Deepak Jaiswal| +| 2. Update the RACM and notificationchannel API so to be OMA compliant, and making sure that we can encapsule PNS in this new specification| Sushanth Hedge/ Padreep Achar | +| 4. Review and accept the previous minutes | Sushanth Hedge/ Padreep Achar | +| 5. Review uploaded files on CAMARA, check the format and provide comments | All | + +## AOB + +* Next meeting will be the *4th of December* + + +--------------------------------------------- + + + diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_231205.md b/original/WebRTC/documentation/MeetingMinutes/MoM_231205.md new file mode 100644 index 0000000000000000000000000000000000000000..da99258a39c7496776086762015407e552cbb79c --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_231205.md @@ -0,0 +1,40 @@ +# MoM - WebRTC Working Group - 231205 + +**Date:** 5/dec/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Elías Pérez (Quobis) +* Benjamin Busvel (Orange) + +## Agenda + +1. Update on YAML files status: [Pull Request #6](https://github.com/camaraproject/WebRTC/pull/6) +2. Discussion current YAML files +3. Next Steps + + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Update on YAML files status | WebRTC WG| Mavenir have been doing some reviews and changes over the comments provided by the participants.| +|Discussion current YAML files| WebRTC WG| Documentation is ready and can be consulted:
                                                                                      • [documentation/API_documentation/webrtc voice api.md](https://github.com/camaraproject/WebRTC/blob/main/documentation/API_documentation/webrtc%20voice%20api.md)
                                                                                        Deepak (TMUS). Proposed changes to be discussed:
                                                                                      • Incorporate the `notficationChannelURI` to the response in the RACM API
                                                                                      • In the RACM API response, add support for multiple MSISDN users (add `msisdn` param (list of MSISDNs the user have launched the service in) within the `connectionInformation` schema as optional). Also add the proper error codes to support this. | +|Next steps| webRTC WG | It is proposed to incorporate the minor changes proposed during the meeting and come up with the first release of the API (version 0.1.0)
                                                                                        For the next release of the API (version 0.1.1) it is proposed to incorporate the handling of multilines-users in the RACM API (depending on complexity this could be incorporated in this release but only for the responses) | + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review the pull request regarding format and update of the repository proposed by Ricardo | Pradeep Achar | +| 2. Review minor changes proposed by Deepak and try to acomodate them | Pradeep Achar | +| 3. Propose commented changes over ther existing Pull Request if needed | Deepak Jaiswal | +| 4. Merge the PR and come up with the first release of the API once all the changes are ready | Ricardo Serrano | +| 5. Review all the repository contributions and provide comments (do not hessitate to open a new issue or a PR if you consider it necessary) | All | + +## AOB +* Next meeting will be the 19th of december diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_231219.md b/original/WebRTC/documentation/MeetingMinutes/MoM_231219.md new file mode 100644 index 0000000000000000000000000000000000000000..1ec1db0c6c97b91b21fd2e6d735629daa2ed1e89 --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_231219.md @@ -0,0 +1,51 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 19/dec/2023 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) + + +## Agenda + + +1. Comments about first release (0.1). First version of the API. +2. Diferents comments about the API + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +| Minutes from last meeting | WebRTC WG | To be Aproved | +| Sucessfull first Api version | WebRTC WG | First version of the API aproval and complete.| +| More aplications for the API | T- Mobile | Propose to develope new features for the API. It is important to implement this first version on the API before looking forward for new funcionalities. It is necesarry to push for the massive adoption that we are looking for.| +CAMARA alignment | T -Mobile | Alignment the API definitions with the CAMARA guidelines (CAMARA falvour) + + + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Check internally new features for the API | all| +| 2. T-Mobile is interested in deploy the API and Telefonica discuss internally | T-Mobile / TEF| +| 3. Review the definitions and alignment with CAMARA guidelines | Ricardo (TEF) | + + + +## AOB + +* Next meeting will be the *16 th of January* + + +--------------------------------------------- + diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_240116.md b/original/WebRTC/documentation/MeetingMinutes/MoM_240116.md new file mode 100644 index 0000000000000000000000000000000000000000..bf9ce8f3bacb763e1823e0a5608592551b1127a7 --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_240116.md @@ -0,0 +1,47 @@ +# MoM - WebRTC Working group - 240116 + +**Date:** 16/Jan/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Deepak Jaiswal (T-Mobile US) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Delon Maxime (Orange) +* Santi Troncoso (Quobis) +* Jesus Pedruelo (Vodafone) + + +## Agenda + +1.WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Comments about general issues commented by Benjamin
                                                                                        1. Review GET status session and look if is mandatory
                                                                                        2. Documentation to clarify who use the API
                                                                                        3. Change status when create a session, the status must not be entered
                                                                                        4. Create a specific yaml file for notification | Orange | Summarize in a pull request all coments did by Benjamin +| Commiting to implement API? | Telefonica
                                                                                          Orange
                                                                                          Vodafone
                                                                                          | Commited to implement but there is not a implementation plan in short time scope | + +In general: Recap all the issues and make and example thorugh a PR in order to diiscuss over this. + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Check internally new features for the API | all | +| 2. Recap all the issues comented in a pull request | Delon/Benjamin (Orange)| +| 3. Documentation and flows API usage | Santi Troncoso (Quobis) & Ricardo Serrano (Telefonica) | + + +## AOB + +* Next meeting will be the *30th of January* + + +--------------------------------------------- diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_240130.md b/original/WebRTC/documentation/MeetingMinutes/MoM_240130.md new file mode 100644 index 0000000000000000000000000000000000000000..a255e8caf87b5c021117fce6733ff51777a454f9 --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_240130.md @@ -0,0 +1,45 @@ +# MoM - WebRTC Working group - 231106 + +**Date:** 30/Jan/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile USA) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Santi Troncoso (Quobis) + + + +## Agenda + +WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Emergency calls | Deepak | As it is a call service, it is mandatory to establish the emergency call service. Emergency parameters should be within the rest of the API params. Location could be an additional/optional parameter. It is good that location parameter will be inside de API parameters to support emergency call service.| +|Issue 2: Update BYON flow doc | Ricardo
                                                                                          Javier
                                                                                          Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                                                          Add autonumbers in the UML format +|Issue 3: Review API response | Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Correct the documentation BYON flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25)| all | +| 5. PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | + +## AOB + +* Next meeting will be the *13rd of February* + diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_240213.md b/original/WebRTC/documentation/MeetingMinutes/MoM_240213.md new file mode 100644 index 0000000000000000000000000000000000000000..48694f2f448b24189d30850c7730b807e27a3fab --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_240213.md @@ -0,0 +1,46 @@ +# MoM - WebRTC Working group - 240213 + +**Date:** 13/Feb/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Pedro Jose Gutierrez (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (Deutsche Telekom) +* Deepak Jaiswal (T-Mobile USA) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) + + + +## Agenda + +WebRTC working group CAMARA Meeting + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Emergency calls | Ricardo and Deepak | Location feature to be stablished at the Operator Network not in GateWay.
                                                                                          ¿It is optional to provide a location parameter? YES.
                                                                                          Get the location in this device model (not tipical mobile device) could be more difficult. It doesnt have location capabilities (such as GPS, or cellular location).
                                                                                          If no location provided user might need to provide it and maybe store it in a separate file to be consulted.| +|Issue 2: Update BYON flow doc | Ricardo
                                                                                          Javier
                                                                                          Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                                                          Add autonumbers in the UML format +|Issue 3: Review API response | Ricardo and Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) +|Issue 5: RACM Session |Deepak | Change session names because some session id names may lead into confusion and URL return - Session id | + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#21](https://github.com/camaraproject/WebRTC/pull/21) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Correct the documentation BYON flow. PUT response to RACH. Make a proposal to change [PR#21](https://github.com/camaraproject/WebRTC/pull/21)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25)| all | +| 5. PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | +|6. RACM session names Pull Request and url to SessionId |Deepak + +## AOB + + * Next meeting will be the *27th of February* \ No newline at end of file diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_240227.md b/original/WebRTC/documentation/MeetingMinutes/MoM_240227.md new file mode 100644 index 0000000000000000000000000000000000000000..fddcacf0b57cf592481e3bda1ab98406b8f177dc --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_240227.md @@ -0,0 +1,43 @@ +# MoM - WebRTC Working group - 240227 + +**Date:** 27/Feb/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (Deutsche Telekom) +* Deepak Jaiswal (T-Mobile USA) +* Santiago Troncoso (Quobis) + + + +## Agenda + +WebRTC working group CAMARA Meeting. Review the diferrents Pull Request + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Update BYON-CallHandling Session | Ricardo and Javier | Reviwed and updated the BYON-CallHandling code. Add 201 (created) response as indicated in HTTP guidelines for a 201 in the PUT session .| +|Issue 2: Update BYON flow doc | Santiago | To be added some missing arrows. Include POST and DELETE of the notification channel flow in the Channel URL (RACM API).
                                                                                          Add autonumbers in the UML format. Review the updated flow doc. Suggest to close the last doc open by Javier and continue with the new one. Separate the doc in two files. +|Issue 3: Review API response | Ricardo and Deepak | PUT response to comply with JSON format [Issue#24](https://github.com/camaraproject/WebRTC/issues/24). Fix description and provide some samples for the clarification. Provide a sample in POST too +|Issue 4: RACM Session |Deepak | Change session names because some session id names may lead into confusion and URL return -> Session id.
                                                                                          The idea is not to create different channels as an app so to the Web RTC gateway we provide this channel and the Web RTC would deliver this notification to this notification channel either using the web book. If the webook web RTC is aware internally about the channel it could use the ID and get how to deliver to the channel. PNS to be explored | + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Review BYON PlantUML flow [PR#27](https://github.com/camaraproject/WebRTC/pull/27) | all| +| 2. Review and accept the minutes [PR#20](https://github.com/camaraproject/WebRTC/pull/20) | Sushanth and Padreep| +| 3. Keep on working in call flow. To be added some missing arrows. [PR#27](https://github.com/camaraproject/WebRTC/pull/27)| Ricardo and Santiago | +| 4. Disccuss Emergency calls [Issue#25](https://github.com/camaraproject/WebRTC/issues/25) | all | +| 5. Correct 201 response (status) [Issue#24](https://github.com/camaraproject/WebRTC/issues/24) | Ricardo | +| 6. RACM session names Pull Request and url to SessionId [PR#29](https://github.com/camaraproject/WebRTC/pull/27) | Deepak | + +## AOB + + * Next meeting will be the *12th of March* + diff --git a/original/WebRTC/documentation/MeetingMinutes/MoM_240312.md b/original/WebRTC/documentation/MeetingMinutes/MoM_240312.md new file mode 100644 index 0000000000000000000000000000000000000000..94c206b0edd8f4b31ba3f698c02a137408c08acb --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/MoM_240312.md @@ -0,0 +1,48 @@ +# MoM - WebRTC Working group - 240312 + +**Date:** 12/March/2024 + +## Attendees + +* Ricardo Serrano (Telefónica) +* Javier Villa (Telefónica) +* Rafał Artych (T-Mobile) +* Deepak Jaiswal (T-Mobile USA) +* Santiago Troncoso (Quobis) +* Pradeep Achar Pushpa (Mavenir) +* Sushanth Hegde (Mavenir) +* Bhabani (Meta) + + + + +## Agenda + +WebRTC working group CAMARA Meeting. Review the diferrents Pull Request + +## Discussion + +| Item | Who | Description | +| ---- | --- | ----------- | +|Issue 1: Update BYO-CallHandling Session | Ricardo and Javier | Updated the BYON-CallHandling code. Update .yaml Gereric201
                                                                                          from: $ref: '#/components/schemas/ObjectResponse'
                                                                                          To: $ref: '#/components/schemas/ReceiverSessionStatus'
                                                                                          [PR#28](https://github.com/camaraproject/WebRTC/pull/28)| +|Issue 2: Update BYON flow doc | Santiago | [Issue#15](https://github.com/camaraproject/WebRTC/issues/15) and [Issue#17](https://github.com/camaraproject/WebRTC/issues/17) Added some missing arrows. Work in progress Separate the doc in two files, Include a simple description of the events in API, and improvement the notification documentation. Add more clarity and action bars. +|Issue 3: RACM Session |Deepak |Updated three yamls files. The primary change in the RACM API is the session ID parameter.
                                                                                          Include additional channel types (Eg:PNS) and change the resource URL to a channel ID. | + + + + +## Action points + +| Description | Who | +| ----------- | --- | +| 1. Upload commit to WebRTC repository with updated Update .yaml Gereric201 | Ricardo and Javier| +| 2. Finish the flow documentation and upload to Camara Github group |Santiago| +| 3. Review changes proposed by Deepack |Sushanth| +| 4. Aproval the minutes and comments if necessary [#PR11](https://github.com/camaraproject/WebRTC/pull/11) and [#PR30](https://github.com/camaraproject/WebRTC/pull/30) | Deepack and Sushanth| + +## AOB + + * Next meeting will be the *26th of March* + * From then to now the minutes will be uploaded to [Confluence](https://wiki.camaraproject.org/display/CAM/Minutes) + +--------- \ No newline at end of file diff --git a/original/WebRTC/documentation/MeetingMinutes/README.md b/original/WebRTC/documentation/MeetingMinutes/README.md new file mode 100644 index 0000000000000000000000000000000000000000..481497ead97bca0673dd672081cbd60636b6177d --- /dev/null +++ b/original/WebRTC/documentation/MeetingMinutes/README.md @@ -0,0 +1,5 @@ +# Meeting notes + +These meetings notes are stored her for archive purposes, find updated Meeting notes at CAMARA main Wiki website + +* https://wiki.camaraproject.org/display/CAM/WebRTC+Meeting+Minutes diff --git a/original/WebRTC/documentation/README.md b/original/WebRTC/documentation/README.md new file mode 100644 index 0000000000000000000000000000000000000000..7149effa98788363bd254398af6c77607dc2dfd3 --- /dev/null +++ b/original/WebRTC/documentation/README.md @@ -0,0 +1,13 @@ +# Documentation + +This folder include extra documentation about the API beyond the technical OpenAPI v3 API description of the `code` folder + +* [MeetingMinutes](MeetingMinutes/) + * Check this folder for the original meeting minutes. + * Newer meeting minutes can be found at [CAMARA Wiki](https://lf-camaraproject.atlassian.net/wiki/spaces/CAM/pages/14564608/WebRTC+Meeting+Minutes) + +* [API_documentation](API_documentation/) + * Check this folder for release status documentation. + +* [SupportingDocuments](SupportingDocuments/) + * Check this folder for extra documentation to support the API definition, UML activity diagrams, API overview description, how to use guides, and other documentation related.. diff --git a/original/WebRTC/documentation/SupportingDocuments/README.md b/original/WebRTC/documentation/SupportingDocuments/README.md new file mode 100644 index 0000000000000000000000000000000000000000..a6e862a91cc5b2950bbdf69d37c6d7312e4088fa --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/README.md @@ -0,0 +1,12 @@ +# Supporting documents + +This folder include documentation to support the API definition, API overview description, how to use guides, and other documentation related with the OpenAPI v3 specs of the `API_definitions` folder. + +* [UML diagrams](uml-diagrams/) + * Check the UML diagrams included for the documented use cases. They include UML activity diagrams that depict a detailed interaction between apps, WebRTC GW and IMS network. + +* [WebRTC voice API](webrtc%20voice%20api.md) + * Check this document for introduction to the API, and brief expanation of the API itself, use cases and status descriptions. + +* [Obtaining a WebRTC SDP to create calls](webrtc-call-handling-sdp-gathering.md) + * CAMARA `webrtc-call-handling` API requires basic usage of the WebRTC API to create calls. You need to obtain and create an `SDP`(Session Description Protocol) body to use in the call creation. This document review that process. diff --git a/original/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW.md b/original/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW.md new file mode 100644 index 0000000000000000000000000000000000000000..08ed05e655203bb84b281cb31e007a0ef946e257 --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/WebRTC-API-User-Story_ASP-WebRTCGW.md @@ -0,0 +1,12 @@ +# WebRTC API User Story (Inbound-Outbound calling: ASP-WebRTC Gateway scenario) + +| **Item** | **Details** | +| --- | --- | +| ***Summary*** | As a web application developer, I want to develop and provide a WebRTC application through an Application Service Provider that enables end users to make and receive calls (outbound and inbound) over the internet using carrier phone numbers.| +| ***Actors and Scope*** | **Actors:** Device Application, Application Servers (API Consumer), Auth Server, WebRTC Gateway (API Provider), Telco Network, Remote Endpoint.
                                                                                          **Scope:**
                                                                                          • Outbound calls: Initiate calls to Remote Endpoints in the Telco Network using phone numbers and establish media sessions.
                                                                                          • Inbound calls: Receive calls from Remote Endpoints in the Telco Network using phone numbers and establish media sessions.
                                                                                          | +| ***Pre-conditions*** | The preconditions are listed below:
                                                                                          • **Device Application:**
                                                                                            • Provided to end users from the Application Service Provider's Application Servers.
                                                                                            • Users are authenticated by the Application Servers provided by the Application Service Provider, and the Device Application and Application Servers are connected via a secure communication channel.
                                                                                          • **Application Servers:**
                                                                                            • Operated by the Application Service Provider and functions as a WebRTC API Consumer. Makes requests to the WebRTC Gateway in response to Device Application requests. Notifications from the WebRTC Gateway to the Application Servers are relayed to specific Device Applications based on their content.
                                                                                            • Authenticates Device Application users with proprietary service IDs and credentials. The connection between Application Servers and Device Applications is protected by a secure communication channel. As a result of end user consent through authentication and authorization using the communication carrier account, tokens for requesting the WebRTC API in response to Device Application requests are issued by the communication carrier.
                                                                                          • **Auth Server:**
                                                                                            • An authentication and authorization server operated by the communication carrier that manages the association between end users utilizing the Device Application and the phone numbers available to those users.
                                                                                            • Performs end user authentication, authorization, and consent using communication carrier accounts, and tokens are issued to Application Servers for accessing the WebRTC API.
                                                                                          • **WebRTC Gateway:**
                                                                                            • A server operated by the carrier that functions as the WebRTC API provider which validates API requests from Application Servers using the Auth Server and provides registration enabling calls using end user phone numbers, call event notifications, and interworking functionality to the Telco Network.
                                                                                          • **Telco Network:**
                                                                                            • The communication carrier's telephony service network, connected to the WebRTC Gateway.
                                                                                          • **Remote Endpoint:**
                                                                                            • An endpoint capable of using the communication carrier's telephony service, connected to and registered with the Telco Network.

                                                                                          See below figure. | +| ***Activities/Steps*** | **Starts when:** In response to a Device Application request, the Application Server prepares to establish a media session with the WebRTC Gateway.

                                                                                          **Step 1:** The Application Server configures event notification subscriptions with the WebRTC Gateway for call state changes and incoming calls for each Device Application.

                                                                                          **Step 2:** The Application Server performs registration with the WebRTC Gateway to enable outbound-call and inbound-call for each Device Application. At this time, the phone number to be used is presented to the Application Server by the WebRTC Gateway.

                                                                                          **Step 3a:** (When the Device Application initiates an outbound-call) In response to a Device Application request, the Application Server sends a media session establishment request to the WebRTC Gateway, specifying the originating and terminating phone numbers. The WebRTC Gateway validates the requested phone numbers and interworks the session establishment request to the Telco Network, while responses from the Telco Network are sent to the Application Server as interworking result event notifications. Once the necessary negotiation is completed, a media session is established between the Device Application and the Remote Endpoint.

                                                                                          **Step 3b:** (When the Device Application receives an inbound-call) When an incoming call arrives from the Telco Network, the WebRTC Gateway sends an incoming call event notification to the Application Server. The Application Server retrieves detailed call information from the WebRTC Gateway and performs the necessary negotiation to establish the media session. Once the necessary negotiation is completed, a media session is established between the Device Application and the Remote Endpoint.

                                                                                          **Ends when:** A call media session is established between the Device Application and the Remote Endpoint.| +| ***Post-conditions*** | When media session state changes (e.g., media modifications) or registration expiration occurs, the WebRTC Gateway sends event notifications to the Application Server, and actions such as renegotiation or registration refresh are performed. The media session terminates when disconnected by either the Device Application or the Remote Endpoint.| +| ***Exceptions*** | Several exceptions might occur during the WebRTC API operations:
                                                                                          - Unauthorized: Invalid credentials (e.g., expired access token).
                                                                                          - Incorrect input data (e.g., malformed phone number).
                                                                                          - Not able to provide: Appropriate event subscriptions and registration have not been performed by the Application Server to initiate outbound-calls or enable inbound-calls reception.| +--- +![fig](./images/fig_user_story_scenario2.png) \ No newline at end of file diff --git a/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README.md b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README.md new file mode 100644 index 0000000000000000000000000000000000000000..2f02816922f3c4d01284769bd0fb070467e0488a --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/README.md @@ -0,0 +1,34 @@ +# WebRTC API call flows + +## 1. General + +This document provides example call flows and messages based on WebRTC API user story for implementers of a WebRTC Gateway that exposes WebRTC APIs and interworks with telco network. + +## 2. Actors + +The involved actors in the call flows are as follows: + +- **Device Application**:A native application or web application running on the user’s device. + +- **Application Server**: Acts as a WebRTC API Invoker. + +- **Auth Server**: Performs auth for API usage in accordance with the CAMARA ICM specification. + +- **WebRTC Gateway**: Acts as a WebRTC API provider, and also interworks with telco network. + +- **Telco Network**: Acts as signalling (SIP) & media servers. + +- **Remote Endpoint**:The peer in the call using the WebRTC API. + + +## 3. List of call flow examples + +The following links provide call flow diagrams and message examples. + +- 3.1. [Subscription for WebRTC events](./subscription_for_webrtc_events.md) +- 3.2. [WebRTC registration](./webrtc_registration.md) +- 3.3. [Call orignation and disconnection](./call_origination_and_disconnection.md) +- 3.4. Call termination and disconnection (TBD) + +The message examples illustrate the fields necessary for implementing a WebRTC Gateway, including all defined optional fields where applicable. +Although the API specification defines fields for [API-design-guidline](https://github.com/camaraproject/Commonalities/blob/main/documentation/API-design-guidelines.md) consistency, those not applicable in the WebRTC API are excluded from the message examples. diff --git a/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection.md b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection.md new file mode 100644 index 0000000000000000000000000000000000000000..9c99517ccfe3ca87075ecea91d9879ed2068dc73 --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/call_origination_and_disconnection.md @@ -0,0 +1,506 @@ +# 3.3. Call origination and disconnection + +This part of the call flows cover call origination from Application Server as WebRTC API Invoker. + +In the call flows, the interface between the WebRTC Gateway and the Telco Network is a SIP-based NNI (Network-to-Network Interface). As such, IMS access-layer procedures (e.g., resource reservation, precondition) are out of scope, while reliable provisional responses (100rel / PRACK) are assumed to be supported on the NNI. + +## 3.3.1. Call origination +### 3.3.1.1. Call flow + +![fig1](./call_origination_and_disconnection_fig-1.png) + +### 3.3.1.2. Example messages + +#### [7] POST /webrtc-call-handling/v0.3/sessions +```http +POST /webrtc-call-handling/v0.3/sessions HTTP/1.1 +Host: webrtc-gw.operator.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000007 +registrationId: reg-550e8400-e29b-41d4-a716-446655440000 + +{ + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + } +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #147 +> +> Related PR: #NN +> +> The current API definition uses a single MediaSessionInformation schema as the message body across multiple operations (POST request/response, GET response, and PUT request/response). However, the set of required properties varies depending on the operation context. This overloading of a single schema reduces clarity and may lead to ambiguity for API consumers regarding which fields are mandatory in each operation. +> +> It is proposed to define distinct schema types corresponding to each operation context (e.g., CreateMediaSessionRequest, CreateMediaSessionResponse, MediaSessionInfo, UpdateMediaSessionRequest, UpdateMediaSessionResponse) in webrtc-callhandling.yaml, and update the $ref references in each operation accordingly. + + +#### [10] SIP INVITE +``` +INVITE sip:+818000000002@tn.operator.com;user=phone SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Supported: 100rel, timer +Allow: INVITE, ACK, BYE, CANCEL, UPDATE, PRACK, OPTIONS +Content-Type: application/sdp +Content-Length: 266 + +v=0 +o=- 8066321617929821805 2 IN IP4 webrtc-gw.operator.com +s=WebRTC-to-SIP Call +c=IN IP4 203.0.113.100 +t=0 0 +m=audio 30000 RTP/AVP 0 8 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:8 PCMA/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [13] SIP 100 Trying +``` +SIP/2.0 100 Trying +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Content-Length: 0 +``` + +#### [14] 201 Created +```http +HTTP/1.1 201 Created +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000007 + +{ + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Initial", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF" +} +``` + +#### [17] SIP 183 Session Progress +``` +SIP/2.0 183 Session Progress +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Require: 100rel +RSeq: 1 +Content-Type: application/sdp +Content-Length: 223 + +v=0 +o=- 4576312012535546667 2 IN IP4 198.51.100.10 +s=SIP Call +c=IN IP4 198.51.100.10 +t=0 0 +m=audio 49170 RTP/AVP 0 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [18] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000016 + +{ + "id": "evt-183-f47ac10b-58cc-4372-a567-0e02b2c3d479", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:01.123Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "InProgress", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "answer": { + "sdp": "v=0\r\no=- 7893214567890123456 2 IN IP4 203.0.113.100\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\nm=audio 50000 UDP/TLS/RTP/SAVPF 111\r\nc=IN IP4 203.0.113.100\r\na=candidate:2098703421 1 udp 2122262783 203.0.113.100 50000 typ host generation 0\r\na=ice-ufrag:B7nX\r\na=ice-pwd:m9sK3jLpQwErT6yHvC2xNfAz\r\na=fingerprint:sha-256 A1:B2:C3:D4:E5:F6:07:18:29:3A:4B:5C:6D:7E:8F:90:01:12:23:34:45:56:67:78:89:9A:AB:BC:CD:DE:EF:F0\r\na=setup:active\r\na=mid:0\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\n" + }, + "reason": "183 Session Progress received from remote endpoint", + "sequenceNumber": 1 + } +} +``` + +#### [20] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000016 +``` + +#### [21] SIP PRACK +``` +PRACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 2 PRACK +RAck: 1 1 INVITE +Content-Length: 0 +``` + +#### [24] SIP 200 OK (PRACK) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack1;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 2 PRACK +Content-Length: 0 +``` + +#### [30] SIP 180 Ringing +``` +SIP/2.0 180 Ringing +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Require: 100rel +RSeq: 2 +Content-Length: 0 +``` + +#### [31] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000027 + +{ + "id": "evt-180-a8b9c0d1-e2f3-4456-b789-0a1b2c3d4e5f", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:02.456Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Ringing", + "reason": "180 Ringing received from remote endpoint", + "sequenceNumber": 2 + } +} +``` + +#### [33] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000027 +``` + +#### [34] SIP PRACK +``` +PRACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack2 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 3 PRACK +RAck: 2 1 INVITE +Content-Length: 0 +``` + +#### [37] SIP 200 OK (PRACK) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776prack2;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 3 PRACK +Content-Length: 0 +``` + +#### [39] SIP 200 OK (INVITE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776asdhds;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 INVITE +Contact: +Allow: INVITE, ACK, BYE, CANCEL, UPDATE, PRACK, OPTIONS +Supported: 100rel, timer +Content-Type: application/sdp +Content-Length: 223 + +v=0 +o=- 4576312012535546667 4 IN IP4 198.51.100.10 +s=SIP Call +c=IN IP4 198.51.100.10 +t=0 0 +m=audio 49170 RTP/AVP 0 101 +a=rtpmap:0 PCMU/8000 +a=rtpmap:101 telephone-event/8000 +a=fmtp:101 0-16 +a=sendrecv +a=ptime:20 +``` + +#### [40] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000035 + +{ + "id": "evt-200-c4d5e6f7-8901-2345-6789-abcdef012345", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:30:05.789Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Connected", + "offer": { + "sdp": "v=0\r\no=- 8066321617929821805 2 IN IP4 0.0.0.0\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=msid-semantic: WMS local-stream\r\nm=audio 42988 UDP/TLS/RTP/SAVPF 111 0 8\r\nc=IN IP4 203.0.113.50\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:1645903805 1 udp 2122262783 203.0.113.50 42988 typ host generation 0\r\na=ice-ufrag:4eKp\r\na=ice-pwd:D4sF5Pv9vx9ggaqxBlHbAFMx\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:C0:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\n" + }, + "answer": { + "sdp": "v=0\r\no=- 7893214567890123456 4 IN IP4 203.0.113.100\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\nm=audio 50000 UDP/TLS/RTP/SAVPF 111\r\nc=IN IP4 203.0.113.100\r\na=candidate:2098703421 1 udp 2122262783 203.0.113.100 50000 typ host generation 0\r\na=ice-ufrag:B7nX\r\na=ice-pwd:m9sK3jLpQwErT6yHvC2xNfAz\r\na=fingerprint:sha-256 A1:B2:C3:D4:E5:F6:07:18:29:3A:4B:5C:6D:7E:8F:90:01:12:23:34:45:56:67:78:89:9A:AB:BC:CD:DE:EF:F0\r\na=setup:active\r\na=mid:0\r\na=sendrecv\r\na=rtcp-mux\r\na=rtpmap:111 opus/48000/2\r\na=fmtp:111 minptime=10;useinbandfec=1\r\n" + }, + "reason": "200 OK received - call connected", + "sequenceNumber": 3 + } +} +``` + +#### [42] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000035 +``` + +#### [43] SIP ACK +``` +ACK sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776ack1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 ACK +Content-Length: 0 +``` + + + + + + + +## 3.3.2. Call termination by call originator +### 3.3.2.1. Sequence + +![fig2](./call_origination_and_disconnection_fig-2.png) + +### 3.3.2.2. Example messages + +#### [53] DELETE /webrtc-call-handling/v0.3/sessions/{mediaSessionId} +```http +DELETE /webrtc-call-handling/v0.3/sessions/0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF HTTP/1.1 +Host: webrtc-gw.operator.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000051 +``` + +#### [56] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000051 +``` + +#### [57] SIP BYE +``` +BYE sip:+818000000002@198.51.100.10:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776bye1 +Max-Forwards: 70 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 4 BYE +Content-Length: 0 +``` + +#### [60] SIP 200 OK (BYE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP webrtc-gw.operator.com:5060;branch=z9hG4bK776bye1;received=203.0.113.100 +From: "Alice" ;tag=1928301774 +To: ;tag=a6c85cf +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 4 BYE +Content-Length: 0 +``` + +#### [61] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000059 + +{ + "id": "evt-bye-d5e6f7a8-b901-2345-6789-abcdef012345", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:35:00.123Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Terminated", + "reason": "Call terminated by originator", + "sequenceNumber": 4 + } +} +``` + +#### [63] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000059 +``` + +## 3.3.3. Call termination by call receiver +### 3.3.3.1. Sequence + +![fig3](./call_origination_and_disconnection_fig-3.png) + +### 3.3.3.2. Example messages + +#### [48] SIP BYE +``` +BYE sip:webrtc-gw.operator.com:5060;transport=tcp SIP/2.0 +Via: SIP/2.0/TCP 198.51.100.10:5060;branch=z9hG4bK889bye1 +Max-Forwards: 70 +From: ;tag=a6c85cf +To: "Alice" ;tag=1928301774 +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 BYE +Content-Length: 0 +``` + +#### [49] SIP 200 OK (BYE) +``` +SIP/2.0 200 OK +Via: SIP/2.0/TCP 198.51.100.10:5060;branch=z9hG4bK889bye1;received=198.51.100.10 +From: ;tag=a6c85cf +To: "Alice" ;tag=1928301774 +Call-ID: a84b4c76e66710@webrtc-gw.operator.com +CSeq: 1 BYE +Content-Length: 0 +``` + +#### [51] POST SINK_URL +```http +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000049 + +{ + "id": "evt-bye-e6f7a8b9-c012-3456-7890-abcdef123456", + "source": "https://webrtc-gw.operator.com", + "type": "org.camaraproject.webrtc-events.v0.session-status", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-02-05T10:35:00.456Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "mediaSessionId": "0AEE1B58BAEEDA3EABA42B32EBB3DFE07E9CFF402EAF9EED8EF", + "originatorAddress": "tel:+818000000001", + "originatorName": "Alice", + "receiverAddress": "tel:+818000000002", + "receiverName": "Bob", + "status": "Terminated", + "reason": "Call terminated by receiver", + "sequenceNumber": 4 + } +} +``` + +#### [53] 204 No Content +```http +HTTP/1.1 204 No Content +x-correlator: a1b2c3d4-e5f6-7890-abcd-000000000049 +``` + + + + + + + + + diff --git a/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events.md b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events.md new file mode 100644 index 0000000000000000000000000000000000000000..0e96d478b7af90efb4421d2e578fa987c361fa9f --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/subscription_for_webrtc_events.md @@ -0,0 +1,267 @@ +# 3.1. Subscription for WebRTC events + +This part of the call flow covers subscribing, unsubscribing, and updating subscriptions for WebRTC events. + +## 3.1.1. Event Subscriptions +### 3.1.1.1. Sequence + +![fig1](./subscription_for_webrtc_events_fig-1.png) + +### 3.1.1.2. Example messages +#### [3] GET /authorize +``` +GET /authorize?response_type=code + &client_id=asp-webrtc-app-001 + &redirect_uri=https%3A%2F%2Fasp.example.com%2Fcallback + &scope=openid%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.session-invitation%3Acreate%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.session-status%3Acreate%20webrtc-events%3Aorg.camaraproject.webrtc-events.v0.registration-ends%3Acreate + &state=af0ifjsldkj + &code_challenge=E9Melhoa2OwvFrEMTJguCHaoeK1t8URWbuGJSstw-cM + &code_challenge_method=S256 HTTP/1.1 +Host: auth.operator.com +``` + +#### [4] 302 Found +``` +HTTP/1.1 302 Found +Location: https://asp.example.com/callback?code=SplxlOBeZQQYbYS6WxSbIA&state=af0ifjsldkj +``` + +#### [6] POST /token +``` +POST /token HTTP/1.1 +Host: auth.operator.com +Content-Type: application/x-www-form-urlencoded + +grant_type=authorization_code +&code=SplxlOBeZQQYbYS6WxSbIA +&redirect_uri=https%3A%2F%2Fasp.example.com%2Fcallback +&code_verifier=dBjftJeZ4CVP-mB92K27uhbUJU1p1r_wW1gFWFOEjXk +``` + +#### [7] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +Cache-Control: no-store + +{ + "access_token": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9.eyJpc3MiOiJodHRwczovL2F1dGgub3BlcmF0b3IuY29tIiwic3ViIjoiKzEyMzQ1Njc4OTAiLCJhdWQiOiJhc3Atd2VicnRjLWFwcC0wMDEiLCJleHAiOjE3MzQyNzI2MDAsImlhdCI6MTczNDI2OTAwMCwic2NvcGUiOiJvcGVuaWQgd2VicnRjLWV2ZW50czpvcmcuY2FtYXJhcHJvamVjdC53ZWJydGMtZXZlbnRzLnYwLnNlc3Npb24taW52aXRhdGlvbjpjcmVhdGUgd2VicnRjLWV2ZW50czpvcmcuY2FtYXJhcHJvamVjdC53ZWJydGMtZXZlbnRzLnYwLnNlc3Npb24tc3RhdHVzOmNyZWF0ZSB3ZWJydGMtZXZlbnRzOm9yZy5jYW1hcmFwcm9qZWN0LndlYnJ0Yy1ldmVudHMudjAucmVnaXN0cmF0aW9uLWVuZHM6Y3JlYXRlIn0.signature", + "token_type": "Bearer", + "expires_in": 3600, + "refresh_token": "tGzv3JOkF0XG5Qx2TlKWIA", + "id_token": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9.eyJpc3MiOiJodHRwczovL2F1dGgub3BlcmF0b3IuY29tIiwic3ViIjoiYWJjZDEyMzQiLCJhdWQiOiJhc3Atd2VicnRjLWFwcC0wMDEiLCJleHAiOjE3MzQyNzI2MDAsImlhdCI6MTczNDI2OTAwMCwibm9uY2UiOiJuLTBTNl9XekEyTWoifQ.signature" +} +``` + +#### [8] POST /webrtc-events-suscription/{apiVersion}/subscriptions +``` +POST /webrtc-events/v0.2/subscriptions HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: b4333c46-49c0-4f62-80d7-f0ef930f1c46 + +{ + "protocol": "HTTP", + "sink": "https://asp.example.com/webhooks/webrtc", + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.abc123", + "accessTokenExpiresUtc": "2025-12-20T23:59:59.999Z", + "accessTokenType": "bearer" + }, + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2025-12-31T23:59:59.999Z" + } +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #135 +> +> Related PR: #NN +> +> Per the updated CAMARA-API-Event-Subscription-and-Notification-Guide.md, event subscriptions (`session-invitation`, `session-status`, `registration-ends`) are consolidated into a single request using the types array to reduce transactions. +> +> This consolidated subscription pattern should be reflected in the webrtc-events.yaml examples. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #76 +> +> Related PR: #NN +> +> The following fields (derived from CAMARA-API-Event-Subscription-and-Notification-Guide) are omitted as they are not applicable to WebRTC events: +> - `subscriptionMaxEvents`: The number of events generated by the WebRTC API cannot be predicted in typical use cases. For resource lifecycle management, `subscriptionExpireTime` is the recommended approach. +> - `initialEvent`: None of the WebRTC events (`session-status`, `session-invitation`, `registration-ends`) are triggered at the event subscription. +> +> Informational descriptions for above fields need to be added in webrtc-events.yaml. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #136 +> +> Related PR: #NN +> +> The webrtc-events.yaml states that `HTTPSubscriptionRequest` and `HTTPSubscriptionResponse` schemas are applied when the `proto` field value is "HTTP", but the current examples do not reflect those schemas. +> +> It should be clarified whether to: +> - Update the examples to conform to the specification, or +> - Remove the schemas above. + +#### [11] 201 Created +``` +HTTP/1.1 201 Created +Content-Type: application/json +x-correlator: b4333c46-49c0-4f62-80d7-f0ef930f1c46 + +{ + "protocol": "HTTP", + "sink": "https://notificationServer.example.com/webhooks/webrtc", + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2025-12-31T23:59:59.999Z" + }, + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "startsAt": "2025-12-15T10:30:00.000Z", + "expiresAt": "2025-12-31T23:59:59.999Z", + "status": "ACTIVE" +} +``` + +## 3.1.2. Refresh event subscriptions +### 3.1.2.1. Sequence + +![fig1](./subscription_for_webrtc_events_fig-2.png) + +### 3.1.2.2. Example messages +#### [18] PUT /webrtc-events-suscription/{apiVersion}/subscriptions/{subscriptionId} +``` +PUT /webrtc-events/v0.2/subscriptions/sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890 HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: f8e7d6c5-b4a3-2190-fedc-ba0987654321 + +{ + "sinkCredential": { + "credentialType": "ACCESSTOKEN", + "accessToken": "eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.xyz789", + "accessTokenExpiresUtc": "2026-01-20T23:59:59.999Z", + "accessTokenType": "bearer" + }, + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2026-01-31T23:59:59.999Z" + } +} +``` +> **ISSUE** (NotAddressed) +> +> Related Issue: #78 +> +> Related PR: #NN +> +> When a `session-status` event subscription expires, signaling for ongoing calls becomes unavailable. Since media modifications may be initiated by the Remote Endpoint, clients MUST refresh the subscription using PUT before `expiresAt` or `sinkCredential.accessTokenExpiresUtc` is reached, if they have ongoing media sessions. +> +> The `PUT` method for subscription refresh must be added to the webrtc-events.yaml. + +#### [21] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: f8e7d6c5-b4a3-2190-fedc-ba0987654321 + +{ + "protocol": "HTTP", + "sink": "https://asp.example.com/webhooks/webrtc", + "types": [ + "org.camaraproject.webrtc-events.v0.session-invitation", + "org.camaraproject.webrtc-events.v0.session-status", + "org.camaraproject.webrtc-events.v0.registration-ends" + ], + "config": { + "subscriptionDetail": { + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2" + }, + "subscriptionExpireTime": "2026-01-31T23:59:59.999Z" + }, + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "startsAt": "2025-12-15T10:30:00.000Z", + "expiresAt": "2026-01-31T23:59:59.999Z", + "status": "ACTIVE" +} +``` + +## 3.1.3. Unsubscribe from events +### 3.1.3.1. Sequence + +![fig3](./subscription_for_webrtc_events_fig-3.png) + +### 3.1.3.2. Example messages +#### [29] DELETE /webrtc-events/{apiVersion}/subscriptions/{subscriptionId} +``` +DELETE /webrtc-events/v0.2/subscriptions/sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890 HTTP/1.1 +Host: api.example.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 +``` + +#### [32] 202 Accepted +``` +HTTP/1.1 202 Accepted +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "id": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890" +} +``` + +#### [33] POST {sink} (callback) +``` +POST /webhooks/webrtc HTTP/1.1 +Host: asp.example.com +Content-Type: application/cloudevents+json +Authorization: Bearer eyJ2ZXIiOiIxLjAiLCJ0eXAiOiJKV1QiLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiIxMjM0NTY3ODkwIn0.xyz789 +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "id": "evt-9a8b7c6d-5e4f-3210-fedc-ba9876543210", + "source": "https://api.example.com/webrtc-events/v0.2", + "type": "org.camaraproject.webrtc-events.v0.subscription-ended", + "specversion": "1.0", + "datacontenttype": "application/json", + "time": "2025-12-15T14:30:00.000Z", + "data": { + "subscriptionId": "sub-a1b2c3d4-e5f6-7890-abcd-ef1234567890", + "terminationReason": "SUBSCRIPTION_DELETED", + "terminationDescription": "Subscription deleted by client request" + } +} +``` + +#### [35] 204 No Content (callback response) +``` +HTTP/1.1 204 No Content +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +``` diff --git a/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration.md b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration.md new file mode 100644 index 0000000000000000000000000000000000000000..58f3eed7905eb1b9169a2779d37023a8873a32fb --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams-APIprovider/webrtc_registration.md @@ -0,0 +1,150 @@ +# 3.2. WebRTC Registration + +This part of the call flow covers WebRTC registration. + +## 3.2.1. WebRTC Registrations +### 3.2.1.1. Sequence + +![fig1](./webrtc_registration_fig1.png) + +### 3.2.1.2. Example messages + +#### [6] POST /webrtc-registration/{apiVersion}/sessions +``` +POST /webrtc-registration/v0.3/sessions HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "deviceId": "7d444840-9dc0-11d1-b245-5ffdce74fad2", + "registrationExpireTime": "2025-12-31T23:59:59.999Z" +} +``` + +> **NOTE** +> +> Depending on the WebRTC registration, SIP REGISTER may either be omitted or performed: +> +> - When the Telco network assigns specific phone number ranges to the WebRTC Gateway and accepts SIP INVITE for call routing, SIP REGISTER is omitted. +> - When a SIP account is issued for each phone number used for interworking from WebRTC, SIP REGISTER is performed. +> +> Even when SIP REGISTER is performed, it should be noted that the WebRTC Gateway does not have a SIM and therefore cannot use AKA′ authentication, making it different from IMS UE Registration. + + + + +#### [9] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: a1b2c3d4-e5f6-7890-abcd-ef1234567890 + +{ + "registrationId": "reg-12345678-abcd-ef90-1234-567890abcdef", + "regInfo": { + "phoneNumber": "+123456789", + "regStatus": "Registered" + }, + "expiresAt": "2025-12-31T23:59:59.999Z" +} +``` + +> **NOTE** +> +> The API Provider may define minimum, maximum, and default values for the WebRTC registration validity period. If the requested duration ("registrationExpireTime" - currentTime) is within the acceptable range, 'expiredAt' may be set to the requested value. +> +> Otherwise, the API Provider may either use (currentTime + default value) for 'expiredAt' or return an error. + + +## 3.2.2. Refresh WebRTC Registrations +### 3.2.2.1. Sequence + +![fig2](./webrtc_registration_fig2.png) + +### 3.2.2.2. Example messages + +#### [15] PUT /webrtc-registration/{apiVersion}/sessions/{registrationId} +``` +PUT /webrtc-registration/v0.3/sessions/reg-12345678-abcd-ef90-1234-567890abcdef HTTP/1.1 +Host: api.example.com +Content-Type: application/json +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "registrationExpireTime": "2026-01-15T12:00:00.000Z" +} +``` + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #144 +> +> Related PR: #NN +> +> The description of the expiration time after update in the PUT operation only considers the case where the API Consumer does not specify a desired expiration time in the PUT request. The description needs to be revised. +> +> Informational descriptions for above need to be revised in webrtc-registration.yaml. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #145 +> +> Related PR: #NN +> +> PUT (update) should be used by the API Consumer to request refreshing existing WebRTC registrations before expiration based on monitoring expiredAt, while POST (new registration) should be used after receiving registration-ends. +> +> Informational descriptions for above need to be added in webrtc-registration.yaml for clarification. + +> **ISSUE** (UnderDiscussion) +> +> Related Issue: #146 +> +> Related PR: #NN +> +> When registration expires, initiating new calls (both incoming and outgoing) is no longer possible. The following behaviors need clarification: +> - Should ongoing media sessions be disconnected? +> - Should any remaining WebRTC event subscription resources associated with the related deviceId be deleted? +> +> If these behaviors are not implementation-dependent, they should be documented as informational descriptions in the webrtc-registration.yaml or webrtc-events.yaml to clarify the expected behavior. + +#### [18] 200 OK +``` +HTTP/1.1 200 OK +Content-Type: application/json +x-correlator: b2c3d4e5-f6a7-8901-bcde-f23456789012 + +{ + "regInfo": { + "phoneNumber": "+123456789", + "regStatus": "Registered" + }, + "registrationId": "reg-12345678-abcd-ef90-1234-567890abcdef", + "expiresAt": "2026-01-15T12:00:00.000Z" +} +``` + +## 3.2.3. WebRTC De-Registrations +### 3.2.3.1. Sequence + +![fig3](./webrtc_registration_fig3.png) + +### 3.2.3.2. Example messages + +#### [24] DELETE /webrtc-registration/{apiVersion}/sessions/{registrationId} +``` +DELETE /webrtc-registration/v0.3/sessions/reg-12345678-abcd-ef90-1234-567890abcdef HTTP/1.1 +Host: api.example.com +Authorization: Bearer eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9... +x-correlator: c3d4e5f6-a7b8-9012-cdef-345678901234 +``` + +#### [27] 204 No Content +``` +HTTP/1.1 204 No Content +x-correlator: c3d4e5f6-a7b8-9012-cdef-345678901234 +``` + + diff --git a/original/WebRTC/documentation/SupportingDocuments/uml-diagrams/README.md b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams/README.md new file mode 100644 index 0000000000000000000000000000000000000000..4a606f19a981453e47987e973e2a3ab6c193e3f8 --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/uml-diagrams/README.md @@ -0,0 +1,26 @@ +# UML diagrams + +This folder includes UML files and PNG rederizations of the three main use cases. + +- [UML diagrams](#uml-diagrams) + - [WebRTC Events sucription](#webrtc-events-sucription) + - [WebRTC Registration process](#webrtc-registration-process) + - [WebRTC Call handling](#webrtc-call-handling) + - [Originating use case (create a call)](#originating-use-case-create-a-call) + - [Terminating use case (receive a call)](#terminating-use-case-receive-a-call) + +## WebRTC Events sucription + +![WebRTC EventsSubscription]() + +## WebRTC Registration process + +![WebRTC Registration]() + +## WebRTC Call handling + +### Originating use case (create a call) +![WebRTC CallHandling ORIG]() + +### Terminating use case (receive a call) +![WebRTC CallHandling TERM]() \ No newline at end of file diff --git a/original/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering.md b/original/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering.md new file mode 100644 index 0000000000000000000000000000000000000000..a2ac9dd93a2a64303e74ce52e98926e3924e6d9d --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/webrtc-call-handling-sdp-gathering.md @@ -0,0 +1,101 @@ +# Obtaining a WebRTC SDP to create calls + +CAMARA `webrtc-call-handling` API requires basic usage of the WebRTC API to create +calls. To put it simply, you need to obtain and create an `SDP`(Session Description +Protocol) body to use in the call creation. + +Let's dig on it on this document. + +Browsers offer the [WebRTC API](https://developer.mozilla.org/en-US/docs/Web/API/WebRTC_API) +that include `getUserMedia()` to obtain access to media devices (microphone and +cameras), and `RTCPeerConnection` interface to create a network connection and +deliver the captured media to a far end. + +That technology becomes responsible of most our common real-time communications on +the web nowadays, from broadcasting to video conference solutions. + +The `RTCPeerConnection` interface, provides an `SDP`that is required by our CAMARA +webrtc-call-handling API. So we are going to explain how to obtain it. + +Here is a simple code that you can test on your browser: + +``` +async function getAudioSDP() { + const config = { iceServers: [{ urls: "stun:stun.l.google.com:19302" }] }; + const peerConnection = new RTCPeerConnection(config); + + try { + // Get the audio stream + const stream = await navigator.mediaDevices.getUserMedia({ audio: true }); + stream.getTracks().forEach(track => peerConnection.addTrack(track, stream)); + + // Create an offer and set it as local description + const offer = await peerConnection.createOffer(); + await peerConnection.setLocalDescription(offer); + + // Collect ICE candidates + const candidates = []; + peerConnection.onicecandidate = (event) => { + if (event.candidate) { + candidates.push(event.candidate); + } else { + // No more candidates, log the result + const sdpData = { + sdp: peerConnection.localDescription.sdp, + candidates: candidates.map(c => c.candidate) + }; + console.log("SDP body:", JSON.stringify(sdpData, null, 2)); + } + }; + } catch (error) { + console.error("Error accessing microphone:", error); + } +} + +// Run the function +getAudioSDP(); +``` + +Maybe it will take a while to resolve the promise, but once you get it, you will +have a valid description for your session using the `SDP`standard +protocol. + +Here is an example of received SDP. You can safely ignore the `candidates` field +and use only the `sdp` value: + +``` +SDP body: { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n", + "candidates": [ + "candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 ufrag YoUo network-cost 999", + "candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 ufrag YoUo network-cost 999" + ] +} +``` + +Since there is a delay between the request and the creation of the peer connection +we can start the call creation using POST, and update the session using PUT and +including the new `SDP`and newer candidates obtained. + +## Using the SDP to create calls + +Here an example of **call creation** using the CAMARA webrtc-call-handling API +with the local `SDP` description gathered on the previous example: + +``` +POST /webrtc-call-handling/v0.2/sessions +{ + "originatorAddress": "tel:+17085852753", + "receiverAddress": "tel:+17085854000", + "offer": { + "sdp": "v=0\r\no=- 4808447918291752114 2 IN IP4 127.0.0.1\r\ns=-\r\nt=0 0\r\na=group:BUNDLE 0\r\na=extmap-allow-mixed\r\na=msid-semantic: WMS 0893fb9b-23c2-4571-a26d-13cb0f4fed9f\r\nm=audio 13765 UDP/TLS/RTP/SAVPF 111 63 9 0 8 13 110 126\r\nc=IN IP4 123.123.123.123\r\na=rtcp:9 IN IP4 0.0.0.0\r\na=candidate:959305279 1 udp 2113937151 26e1f6e6-f0cb-47fb-a1b4-afa62b6a7f29.local 50745 typ host generation 0 network-cost 999\r\na=candidate:3375440286 1 udp 1677729535 123.123.123.123 13765 typ srflx raddr 0.0.0.0 rport 0 generation 0 network-cost 999\r\na=ice-ufrag:YoUo\r\na=ice-pwd:kK5J6IAgiKFDFU+2rC+FyZal\r\na=ice-options:trickle\r\na=fingerprint:sha-256 CF:56:D8:57:9B:68:B2:1C:F6:ED:6C:CO:02:7C:96:C2:88:A3:C2:38:AD:A2:CA:F5:0D:47:BB:81:74:7B:75:17\r\na=setup:actpass\r\na=mid:0\r\na=extmap:1 urn:ietf:params:rtp-hdrext:ssrc-audio-level\r\na=extmap:2 http://www.webrtc.org/experiments/rtp-hdrext/abs-send-time\r\na=extmap:3 http://www.ietf.org/id/draft-holmer-rmcat-transport-wide-cc-extensions-01\r\na=extmap:4 urn:ietf:params:rtp-hdrext:sdes:mid\r\na=sendrecv\r\na=msid:0893fb9b-23c2-4571-a26d-13cb0f4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\na=rtcp-mux\r\na=rtcp-rsize\r\na=rtpmap:111 opus/48000/2\r\na=rtcp-fb:111 transport-cc\r\na=fmtp:111 minptime=10;useinbandfec=1\r\na=rtpmap:63 red/48000/2\r\na=fmtp:63 111/111\r\na=rtpmap:9 G722/8000\r\na=rtpmap:0 PCMU/8000\r\na=rtpmap:8 PCMA/8000\r\na=rtpmap:13 CN/8000\r\na=rtpmap:110 telephone-event/48000\r\na=rtpmap:126 telephone-event/8000\r\na=ssrc:932268938 cname:mzxQSFSDV3JpfIJY\r\na=ssrc:932268938 msid:0893fb9b-23c2-4571-a26d-13ccof4fed9f 2daf5a1e-d3bf-4d4e-95db-b8623fce4176\r\n" + }, + "clientCorrelator": "fda6e26d-e7c8-4596-870c-c083c0d39b2c" +} +``` + +Check extra information about this API on the inline YAML documentation or refer +to other supporting documents within this folder. + +Happy webrtc-ing! + diff --git a/original/WebRTC/documentation/SupportingDocuments/webrtc_voice_api.md b/original/WebRTC/documentation/SupportingDocuments/webrtc_voice_api.md new file mode 100644 index 0000000000000000000000000000000000000000..80731605c46aabd27e007c85360d74725d016b91 --- /dev/null +++ b/original/WebRTC/documentation/SupportingDocuments/webrtc_voice_api.md @@ -0,0 +1,129 @@ +# Overview + +Bring your own number (BYON) service aims to provide consumers with the ability to use their phone number (MSISDN) for outgoing and incoming calls from non-SIM card devices. To access the service, users are required to authenticate using their digital credentials associated with their MNO account, in example their operator app credentials. As registration from a web endpoint is necessary to enable the service on non-SIM card devices. + +Outgoing calls made through the service will display the user's MSISDN as the caller number, ensuring that the recipient recognizes the user's phone number on their caller ID. + +Incoming calls introduce a unique functionality whereby multiple devices will ring simultaneously. This includes the user's smartphone and the web endpoint they have registered from. This design enables users to conveniently answer calls from any of these devices, depending on their preference or accessibility. The service is compatible with various devices that support web browsing environments, such as laptops, PCs, and XR immersive glasses. + +The service specification emphasises the accessibility and flexibility of utilising one's phone number across different non-SIM card devices. By leveraging this web-based service, users can extend their communication capabilities beyond traditional SIM-based devices, enhancing their overall communication experience. + +## Introduction + +This service brings new functionalities for the WebRTC services whose idea is to integrate BYON API to maintain the client number in out-bound and in-bound calls from web comms service. + +**Out-bound calls:** + +- Recipient receives call as if it was from User's normal phone number. +- Maintains common number through web communication service and standard subscription. +- Facilitates number recognition and call-back for co-workers, partners and/or clients. + +**In-bound calls:** + +- Receive phone calls simultaneously on phone subscription and web communication service. +- Presents 'Occupied user' info to caller user is already in phone call. +- Facilitates common multi-channel contact with co-workers, partners and/or clients. + +## API Spec + +### Roles, Actors and Scope + +Roles: Customer-user + +Actors: Application service providers, hyperscalers, application developers. + +Scope: + +1. Register to Network – Register the client endpoint instance to MNO's IMS Network. +2. Create Notification Channel – Create Notification channel of specified type to receive notifications from the network (e.g. incoming call). +3. Place an Out Call – Place an outbound voice call request to the MNO's IMS Network. +4. Receive an Incoming Call - Receive an incoming call request from the MNO's IMS network. + +### Authentication and Authorization + +The defined APIs uses OAUTH 2.0 client credentials and uses the Access Token granted by the CSP's IDP for its usage. This must be the initial procedure to be completed before invoking any of the service APIs. + +### Pre-Conditions + +The preconditions are listed below: + +- The customer-user must have operator/MNO (provider of the native MSISDN) provided credentials to login to the web app. + +### Activities/Steps + +- Starts when: The customer-user logs into the communication application in the browser. +- Ends when: The customer-user logs out of the communication application in the browser or closes the browser. + +### Post-Conditions + +The customer-user places an outgoing voice call or accepts an incoming voice call. + +### Exceptions + +Several exceptions might occur during the API operations, + +- Unauthorized: Invalid credentials. +- \ + +### API Endpoint details + +**Registration and Connection Management (RACM)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /session | Create a RACM session | Registers the client instance into MNO's IMS Network via the WebRTC Gateway. This request will include the Access Token received from the MNO's IDP (auth server).On successful RACM session creation, the client endpoint reusing the device's MSISDN will be successfully registered in MNO's IMS network, ready to accept any call origination or termination request. | +| PUT /session/{sessionId} | Modify a RACM session | This modification request is to share refreshed Access Token received from MNO's IDP (auth server). | +| DELETE /session/{sessionId} | Delete a RACM session | When the customer-user gracefully logs out of the application, the RACM session will be deleted, resulting in de-registration from the MNO's IMS network. | + +**Notification Channel Management** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /channels | Create a Notification channel | Creates a notification channel of specified type (e.g. Websocket, PNS, webhook) in order to receive notifications from the network. These notification channels will be used to send following notifications from the network, +- Incoming call (network -\> client) +- Any other notifications from the network such as call setup status, call modification status, etc. + | + +**OneToOne Call (outgoing)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| POST /session | Create a Voice session | Create an Outbound (1-1) Voice session. This request when received at the WebRTC GW triggers an outgoing call request into the MNO's IMS network. The call setup status (inprogress, ringing, connected, release) is sent over the websocket notification channel. | +| PUT /session/{sessionId}/status | Modify a Voice session | This modification request is to modify the call object attributes such as media properties included in the SDP (e.g. call placed on hold). | +| DELETE /session/{sessionId} | Delete a Voice session | When the call is released from the client's end, the corresponding Voice session object is deleted, which will trigger the WebRTC GW to initiate a Call release into the CSP's IMS network. | +| | | When the call is released from the network's end, the call release notification is sent over the websocket notification channel, which will result in deleting of the Voice session object. | + +**OneToOne Call (incoming)** + +| Endpoint | Operation | Description | +| --- | --- | --- | +| | | Notification for inbound call is received via the websocket notification channel. The Voice session object is created by default prior to sending this inbound call notification. | +| PUT /session/{sessionId}/status | Modify a Voice session | This modification request is to modify the call object attributes such as media properties included in the SDP (e.g. call placed on hold). | +| DELETE /session/{sessionId} | Delete a Voice session | When the call is terminated from the client's end, the corresponding Voice session object is deleted, which will trigger the WebRTC GW to initiate a Call release into the MNO's IMS network. | +| | | When the call is released from the network's end, the call release notification is sent over the websocket notification channel, which will result in deleting of the Voice session object. | + +### Event status enumeration + +There are defined a series of status for the call. These status are used by the session endpoint for PUT actions and also used by the event notification channel. + +Status are: + +| Status | SIP Response | Description | +| ------ | ------------ | ----------- | +`Initial` | n/a | Initial status of transaction +`InProgress` | 183 Session progress | Updated info about a session +`Ringing` | 180 Ringing | Destination user agent is alerting the user +`Proceding` | n/a | Call progressing +`Connected` | 200 OK | Session in place +`Terminated` | n/a | The call is being terminated, but not defined the reason. It needs to add a "reason" +`Hold` | n/a | Status when a call on hold +`Resume` | n/a | Status for a call that is resumed +`SessionCancelled` | n/a | 487 Resquest terminated or CANCEL+200OK +`Declined` | 603 Decline | The destination does not want to participate +`Failed` | 412 / 430 | Call terminated and failed without 200 OK +`Waiting` | 182 Queued | Call pending to be processed +`NoAnswer` | 408 Request Timeout | No answer before timer expires +`NotReachable` | 404 Not found | Destination requested not found +`Busy` | 486 Busy here | Callee is busy + +Ref. for status mapping: https://www.gsma.com/newsroom/wp-content/uploads//NG.114-v1.0-3.pdf \ No newline at end of file diff --git a/original/eSimRemoteManagement/README.md b/original/eSimRemoteManagement/README.md new file mode 100644 index 0000000000000000000000000000000000000000..fcd43cba0ba6b713fb1709465988ae804661f714 --- /dev/null +++ b/original/eSimRemoteManagement/README.md @@ -0,0 +1,42 @@ + + + + + + + + + +# eSimRemoteManagement + +Sandbox API Repository to describe, develop, document, and test the eSimRemoteManagement Service API(s). The repository does not yet belong to a CAMARA Sub Project. + +* API Repository [wiki page](https://lf-camaraproject.atlassian.net/wiki/x/K4CbFg) + +## Scope + +* Service API(s) “eSimRemoteManagement” (see APIBacklog.md) +* The API(s) provide(s) the API consumer with the ability to: + * Provide eSIM-based remote management capability, allowing users to remotely manage the status of profiles on the device's eUICC and complete remote operations such as downloading, activating, de-activating or deleting. +* Describe, develop, document, and test the API(s) +* Started: December 2025 + + + + + +## Release Information + +The repository has no (pre)releases yet, work in progress is within the main branch. + + + +## Contributing + +* Meetings are held virtually + * Schedule: Weekly on Thursday 16:00 CST / 10:00 CEST + * [Registration / Join](https://zoom-lfx.platform.linuxfoundation.org/meeting/96461951353?password=150ba7bb-550f-40f6-b8b2-82e67d36ac4e) + * Minutes: Access [Meeting minutes](https://wiki.camaraproject.org/display/CAM/eSIMRemoteManagement) +* Mailing List + * Subscribe / Unsubscribe to the mailing list of this Sub Project . + * A message to the community of this Sub Project can be sent using . \ No newline at end of file diff --git a/original/eSimRemoteManagement/code/API_definitions/README.MD b/original/eSimRemoteManagement/code/API_definitions/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..3129dfd83b83c16bdb3ff2b362c8bb0ae28fb37c --- /dev/null +++ b/original/eSimRemoteManagement/code/API_definitions/README.MD @@ -0,0 +1 @@ +Here you can add your definition file(s). Delete this README.MD file after the first file is added. diff --git a/original/eSimRemoteManagement/code/API_definitions/esim-remote-management.yaml b/original/eSimRemoteManagement/code/API_definitions/esim-remote-management.yaml new file mode 100644 index 0000000000000000000000000000000000000000..f4b4f32b1bbeaac70fd10d6c35e90b8d96024b2f --- /dev/null +++ b/original/eSimRemoteManagement/code/API_definitions/esim-remote-management.yaml @@ -0,0 +1,854 @@ +--- +openapi: 3.0.3 +info: + title: eSIM Remote Management + description: > + Provide eSIM-based remote management capability, allowing users to remotely manage the status of profiles on the device's eUICC and complete remote operations such as downloading, activating, de-activating or deleting. + + # Introduction + + The eIM Platform API provides a comprehensive, secure, and standardized interface for device manufacturers (OEMs) and ecosystem partners to remotely manage eSIM profiles on connected devices. This API empowers you to offer seamless connectivity lifecycle management directly within your device ecosystem. + + # API Functionality + + The API provides the following functionality: + - Profile Download & Installation: Securely provision and download new eSIM profiles to devices, based on user subscription, geographic location, or specific business triggers. + - Profile Inventory Query: Retrieve a detailed list of all eSIM profiles currently stored on a device, including their status (e.g., enabled, disabled, pending download), associated ICCID/EID, and service provider information. + - Profile Lifecycle Management: Execute precise control over installed profiles: + - Activation/Enable: Switch a downloaded profile to the active state for live connectivity. + - Deactivation/Disable: Temporarily disable a profile without deleting it from the device. + - Deletion: Permanently remove an unused or obsolete profile from the device's eSIM chip, freeing up memory. + + # Authorization and authentication + + The "Camara Security and Interoperability Profile" provides details of how an API consumer requests an access token. Please refer to Identity and Consent Management (https://github.com/camaraproject/IdentityAndConsentManagement/ ) for the released version of the profile. + + The specific authorization flows to be used will be agreed upon during the onboarding process, happening between the API consumer and the API provider, taking into account the declared purpose for accessing the API, whilst also being subject to the prevailing legal framework dictated by local legislation. + + In cases where personal data is processed by the API and users can exercise their rights through mechanisms such as opt-in and/or opt-out, the use of three-legged access tokens is mandatory. This ensures that the API remains in compliance with privacy regulations, upholding the principles of transparency and user-centric privacy-by-design. + + # Additional CAMARA error responses + + The list of error codes in this API specification is not exhaustive. Therefore the API specification may not document some non-mandatory error statuses as indicated in `CAMARA API Design Guide`. + + Please refer to the `CAMARA_common.yaml` of the Commonalities Release associated to this API version for a complete list of error responses. The applicable Commonalities Release can be identified in the `API Readiness Checklist` document associated to this API version. + + As a specific rule, error `501 - NOT_IMPLEMENTED` can be only a possible error response if it is explicitly documented in the API. + version: wip + x-camara-commonalities: 0.6 + license: + name: Apache 2.0 + url: https://www.apache.org/licenses/LICENSE-2.0.html +externalDocs: + description: Project documentation at CAMARA + url: https://github.com/camaraproject/eSimRemoteManagement +servers: + - url: "{apiRoot}/eSimRemoteManagement/vwip" + variables: + apiRoot: + default: http://localhost:9091 + description: API root +tags: + - name: eSIMRemoteManagement + description: API operation to eSIM Remote Management +paths: + /profile/list-syn: + post: + security: + - openId: + - esim-remote-management:listSyn + tags: + - eSIMRemoteManagement + operationId: profileListSyn + summary: Profile List Synchronization + description: Synchronize Profile list + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + /profile/status/enquiry: + post: + security: + - openId: + - esim-remote-management:enquiry + tags: + - eSIMRemoteManagement + operationId: profileStatusEnquiry + summary: Profile Status Enquiry + description: Query Profile status + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + timestamp: + type: string + description: Request timestamp + sequenceNum: + type: string + description: Sequence number + clientId: + type: string + description: Client ID + data: + type: object + properties: + iccid: + type: string + description: ICCID + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + data: + type: object + properties: + eId: + type: string + description: EID + isUsed: + type: integer + description: Profile usage status 0 Not used, 1 Used + default: 0 + maxUsedCount: + type: integer + description: Maximum download count for Profile + default: 1 + usedCount: + type: integer + description: Usage count of Profile + default: 0 + modifyTime: + type: string + description: Modification time + /profile/set/fallback/attribute: + post: + security: + - openId: + - esim-remote-management:attribute + tags: + - eSIMRemoteManagement + operationId: profileSetFallbackAttribute + requestBody: + required: true + content: + application/json: + schema: + type: object + properties: + timestamp: + type: string + description: Request timestamp + sequenceNum: + type: string + description: Sequence number + clientId: + type: string + description: Client ID + data: + type: object + properties: + eId: + type: string + description: EID + imei: + type: string + description: Device ID + iccid: + type: string + description: ICCID to operate on + responses: + '200': + description: Success response + content: + application/json: + schema: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + data: + type: object + properties: + taskId: + type: string + description: Task ID + /profile/result/query: + post: + security: + - openId: + - esim-remote-management:query + tags: + - eSIMRemoteManagement + operationId: profileResultQuery + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileResultQueryReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileResultQueryResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/oper: + post: + security: + - openId: + - esim-remote-management:oper + tags: + - eSIMRemoteManagement + operationId: profileOperation + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileOperReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileOperResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/downloaded-list: + post: + security: + - openId: + - esim-remote-management:downloadedlist + tags: + - eSIMRemoteManagement + operationId: profileList + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqEIdProfileListReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespEIdProfileListResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /profile/download: + post: + security: + - openId: + - esim-remote-management:download + tags: + - eSIMRemoteManagement + operationId: profileDownload + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqProfileDownloadReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespProfileDownloadResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' + /eid-status-enquiry: + post: + security: + - openId: + - esim-remote-management:enquiry + tags: + - eSIMRemoteManagement + operationId: eIdStatusEnquiry + requestBody: + content: + application/json: + schema: + $ref: '#/components/schemas/BaseCmpReqEIdStatusEnquiryReq' + required: true + responses: + "200": + description: OK + content: + '*/*': + schema: + $ref: '#/components/schemas/BaseCmpRespEIdStatusEnquiryResp' + '400': + $ref: '#/components/responses/Generic400' + '401': + $ref: '#/components/responses/Generic401' + '403': + $ref: '#/components/responses/Generic403' + '404': + $ref: '#/components/responses/Generic404' + '500': + $ref: '#/components/responses/Generic500' + '503': + $ref: '#/components/responses/Generic503' +components: + securitySchemes: + openId: + type: openIdConnect + description: to support Consent Management + openIdConnectUrl: https://example.com/.well-known/openid-configuration + parameters: + x-correlator: + name: x-correlator + in: header + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + pattern: ^[a-zA-Z0-9-]{1,55}$ + schemas: + BaseCmpReqProfileResultQueryReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + description: Client ID + data: + $ref: '#/components/schemas/ProfileResultQueryReq' + ProfileResultQueryReq: + type: object + properties: + taskId: + type: string + BaseCmpRespProfileResultQueryResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/ProfileResultQueryResp' + ProfileResultQueryResp: + type: object + properties: + taskId: + type: string + imei: + type: string + iccid: + type: string + operResult: + type: integer + description: 'Operation profile result: + - 0: executing. + - 1: Operation success. + - 2: Operation fail.' + enum: [0, 1, 2] + eId: + type: string + resultMsg: + type: string + description: Result message + BaseCmpReqProfileOperReq: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + $ref: '#/components/schemas/ProfileOperReq' + ProfileOperReq: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + optType: + type: integer + description: Operation type 1 Enable, 2 Disable, 3 Delete + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpRespProfileOperResp: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + $ref: '#/components/schemas/ProfileOperResp' + ProfileOperResp: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + optType: + type: integer + description: Operation type 1 Enable, 2 Disable, 3 Delete + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpReqEIdProfileListReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + description: Client ID + data: + $ref: '#/components/schemas/EIdProfileListReq' + EIdProfileListReq: + type: object + properties: + eId: + type: string + BaseCmpRespEIdProfileListResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/EIdProfileListResp' + EIdProfileListResp: + type: object + properties: + imei: + type: string + profiles: + type: array + items: + $ref: '#/components/schemas/ProfileInfo' + eId: + type: string + ProfileInfo: + type: object + properties: + iccid: + type: string + enableStatus: + type: integer + format: int32 + BaseCmpReqProfileDownloadReq: + type: object + properties: + protocol: + type: string + description: Protocol type + sink: + type: string + description: Callback address (sink address for notification reception) + types: + type: array + items: + type: string + description: List of subscribed event types + config: + $ref: '#/components/schemas/ProfileDownloadReq' + ProfileDownloadReq: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + autoEnableType: + type: integer + description: Download and activate option 1 Download and enable + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpRespProfileDownloadResp: + type: object + properties: + code: + type: integer + description: Response code + message: + type: string + description: Response message + config: + $ref: '#/components/schemas/ProfileDownloadResp' + ProfileDownloadResp: + type: object + properties: + subscriptionDetail: + type: object + properties: + eId: + type: string + description: Device EID + imei: + type: string + description: Device IMEI number + iccid: + type: string + description: Card ICCID number + autoEnableType: + type: integer + description: Download and activate option 1 Download and enable + initialEvent: + type: boolean + description: Whether to send initial event + subscriptionMaxEvents: + type: integer + description: Maximum subscription events + subscriptionExpireTime: + type: string + description: Subscription expiration time + BaseCmpReqEIdStatusEnquiryReq: + type: object + properties: + timestamp: + type: string + sequenceNum: + type: string + clientId: + type: string + data: + $ref: '#/components/schemas/EIdStatusEnquiryReq' + EIdStatusEnquiryReq: + type: object + properties: + eId: + type: string + BaseCmpRespEIdStatusEnquiryResp: + type: object + properties: + resultCode: + type: string + description: 'B100000 - success other - fail' + resultDesc: + type: string + sequenceNum: + type: string + data: + $ref: '#/components/schemas/EIdStatusEnquiryResp' + EIdStatusEnquiryResp: + type: object + properties: + enableIccid: + type: string + imei: + type: string + syncTime: + type: string + eId: + type: string + ErrorInfo: + type: object + required: + - status + - code + - detail + properties: + status: + type: integer + description: HTTP response status code + code: + type: string + description: Code given to this error + detail: + type: string + description: Detailed error description + responses: + Generic400: + description: Problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 400 + code: INVALID_ARGUMENT + detail: Client specified an invalid argument, request body or query param + Generic401: + description: Authentication problem with the client request + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 401 + code: UNAUTHENTICATED + detail: Request not authenticated due to missing, invalid, or expired credentials + Generic403: + description: Client does not have sufficient permission + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + examples: + PermissionDenied: + value: + status: 403 + code: PERMISSION_DENIED + detail: Client does not have sufficient permissions to perform this action + InvalidTokenContext: + value: + status: 403 + code: INVALID_TOKEN_CONTEXT + detail: Phone number cannot be deducted from access token context + Generic404: + description: Resource Not Found + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 404 + code: NOT_FOUND + detail: A specified resource is not found + Generic500: + description: Server error + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 500 + code: INTERNAL + detail: Server error + Generic503: + description: Service unavailable. Typically the server is down. + headers: + x-correlator: + description: Correlation id for the different services + schema: + type: string + content: + application/json: + schema: + $ref: '#/components/schemas/ErrorInfo' + example: + status: 503 + code: UNAVAILABLE + detail: Service unavailable diff --git a/original/eSimRemoteManagement/documentation/API_documentation/README.MD b/original/eSimRemoteManagement/documentation/API_documentation/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/eSimRemoteManagement/documentation/API_documentation/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory. diff --git a/original/eSimRemoteManagement/documentation/SupportingDocuments/README.MD b/original/eSimRemoteManagement/documentation/SupportingDocuments/README.MD new file mode 100644 index 0000000000000000000000000000000000000000..f71c2a667b84b38512f5893a2240aef980329112 --- /dev/null +++ b/original/eSimRemoteManagement/documentation/SupportingDocuments/README.MD @@ -0,0 +1 @@ +This README.MD can be deleted when the first file is added to this directory.